Upgrade to Pro — share decks privately, control downloads, hide ads and more …

AI-Driven Cloud Defense: Integrating Microsoft ...

AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure AI

Cloud-native attacks are accelerating, with adversaries using automation and AI to outpace traditional defenses.

Security teams face alert fatigue, manual investigations, and slow response times—creating a dangerous protection gap.

This session will demonstrate how Microsoft Security Copilot, combined with Azure AI services like OpenAI, Cognitive Search, and anomaly detection, transforms cloud defense.

Through demos and real-world integration patterns with Sentinel, Logic Apps, and Power Automate, I will show how AI enables faster detection, smarter threat hunting, and automated incident response.

Avatar for Aleem Isiaka

Aleem Isiaka

October 17, 2025
More Decks by Aleem Isiaka

Other Decks in Technology
Transcript

  1. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Aleem Isiaka Software Engineer x.com/limistah github.com/limistah limistah.dev linkedin.com/in/limistah
  2. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

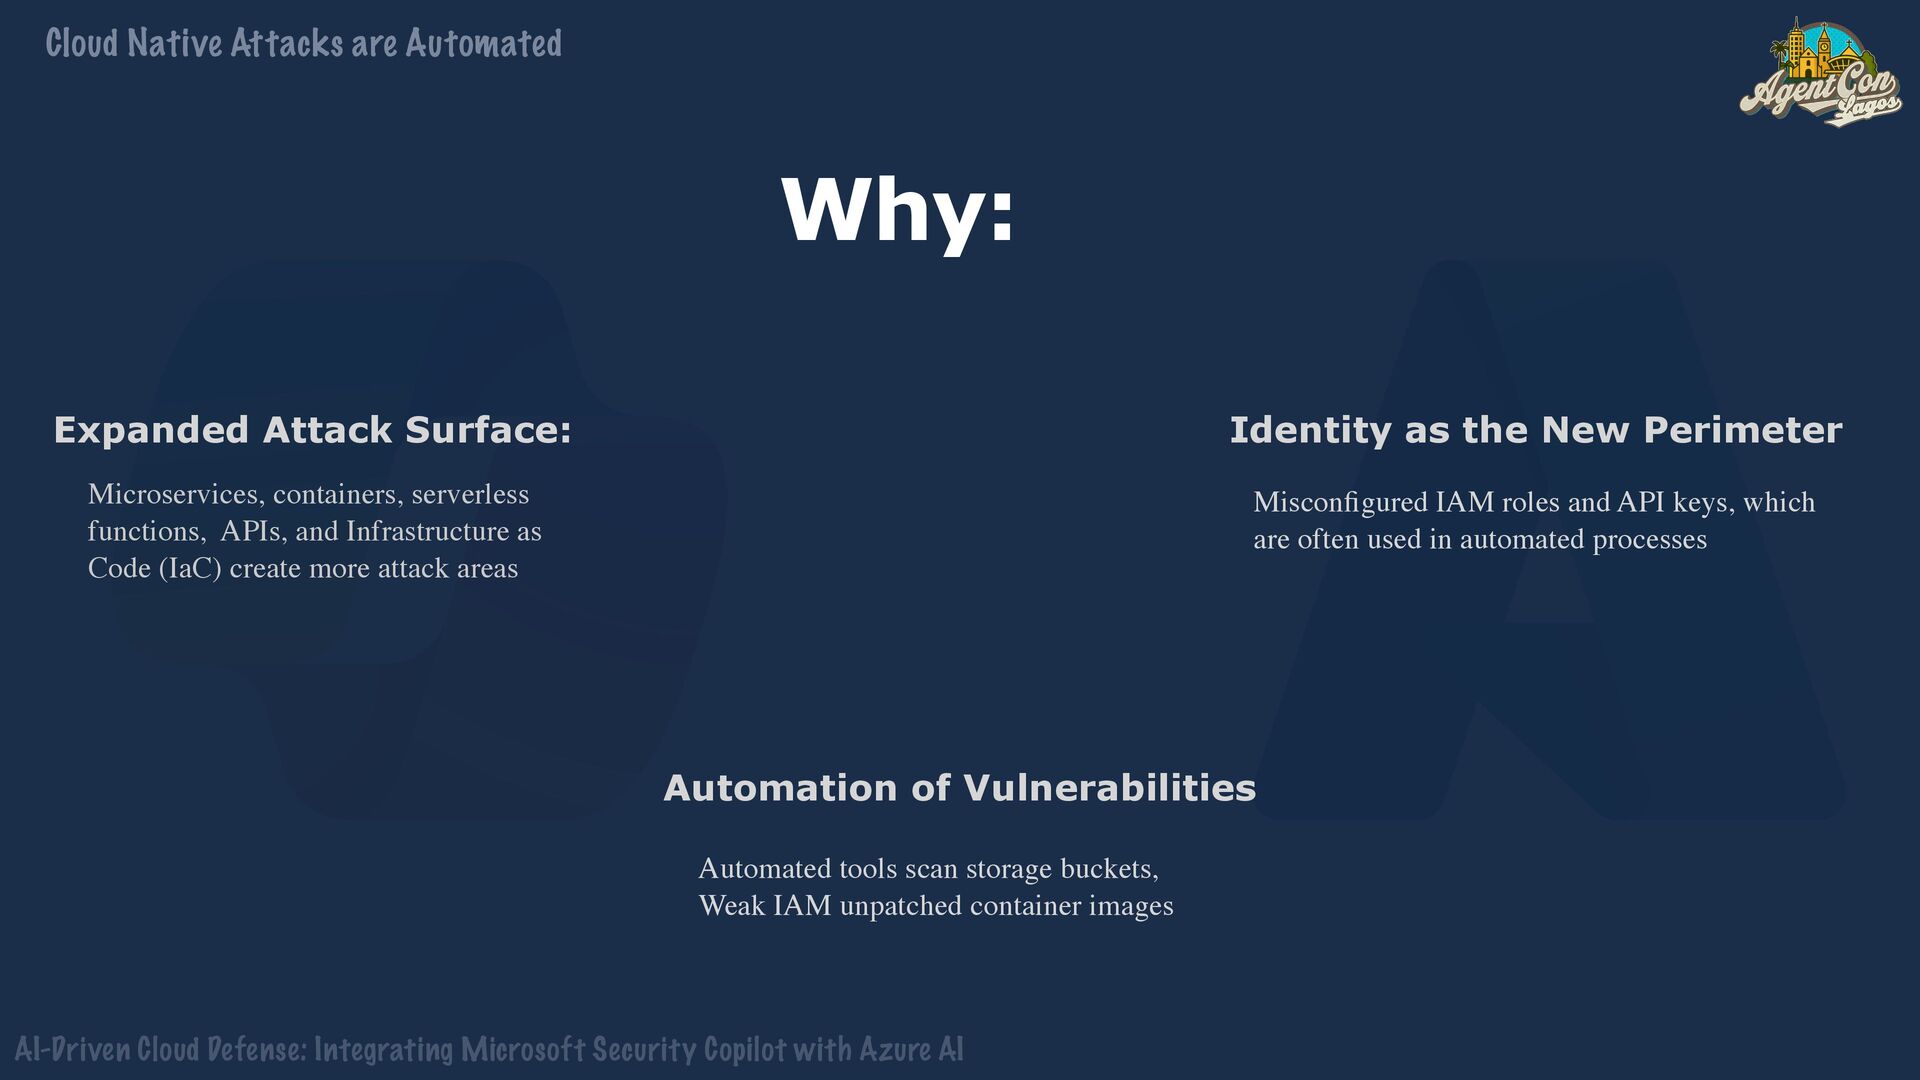
    AI Why: Cloud Native Attacks are Automated Expanded Attack Surface: Automation of Vulnerabilities Identity as the New Perimeter Microservices, containers, serverless functions, APIs, and Infrastructure as Code (IaC) create more attack areas Automated tools scan storage buckets, Weak IAM unpatched container images Miscon fi gured IAM roles and API keys, which are often used in automated processes
  3. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

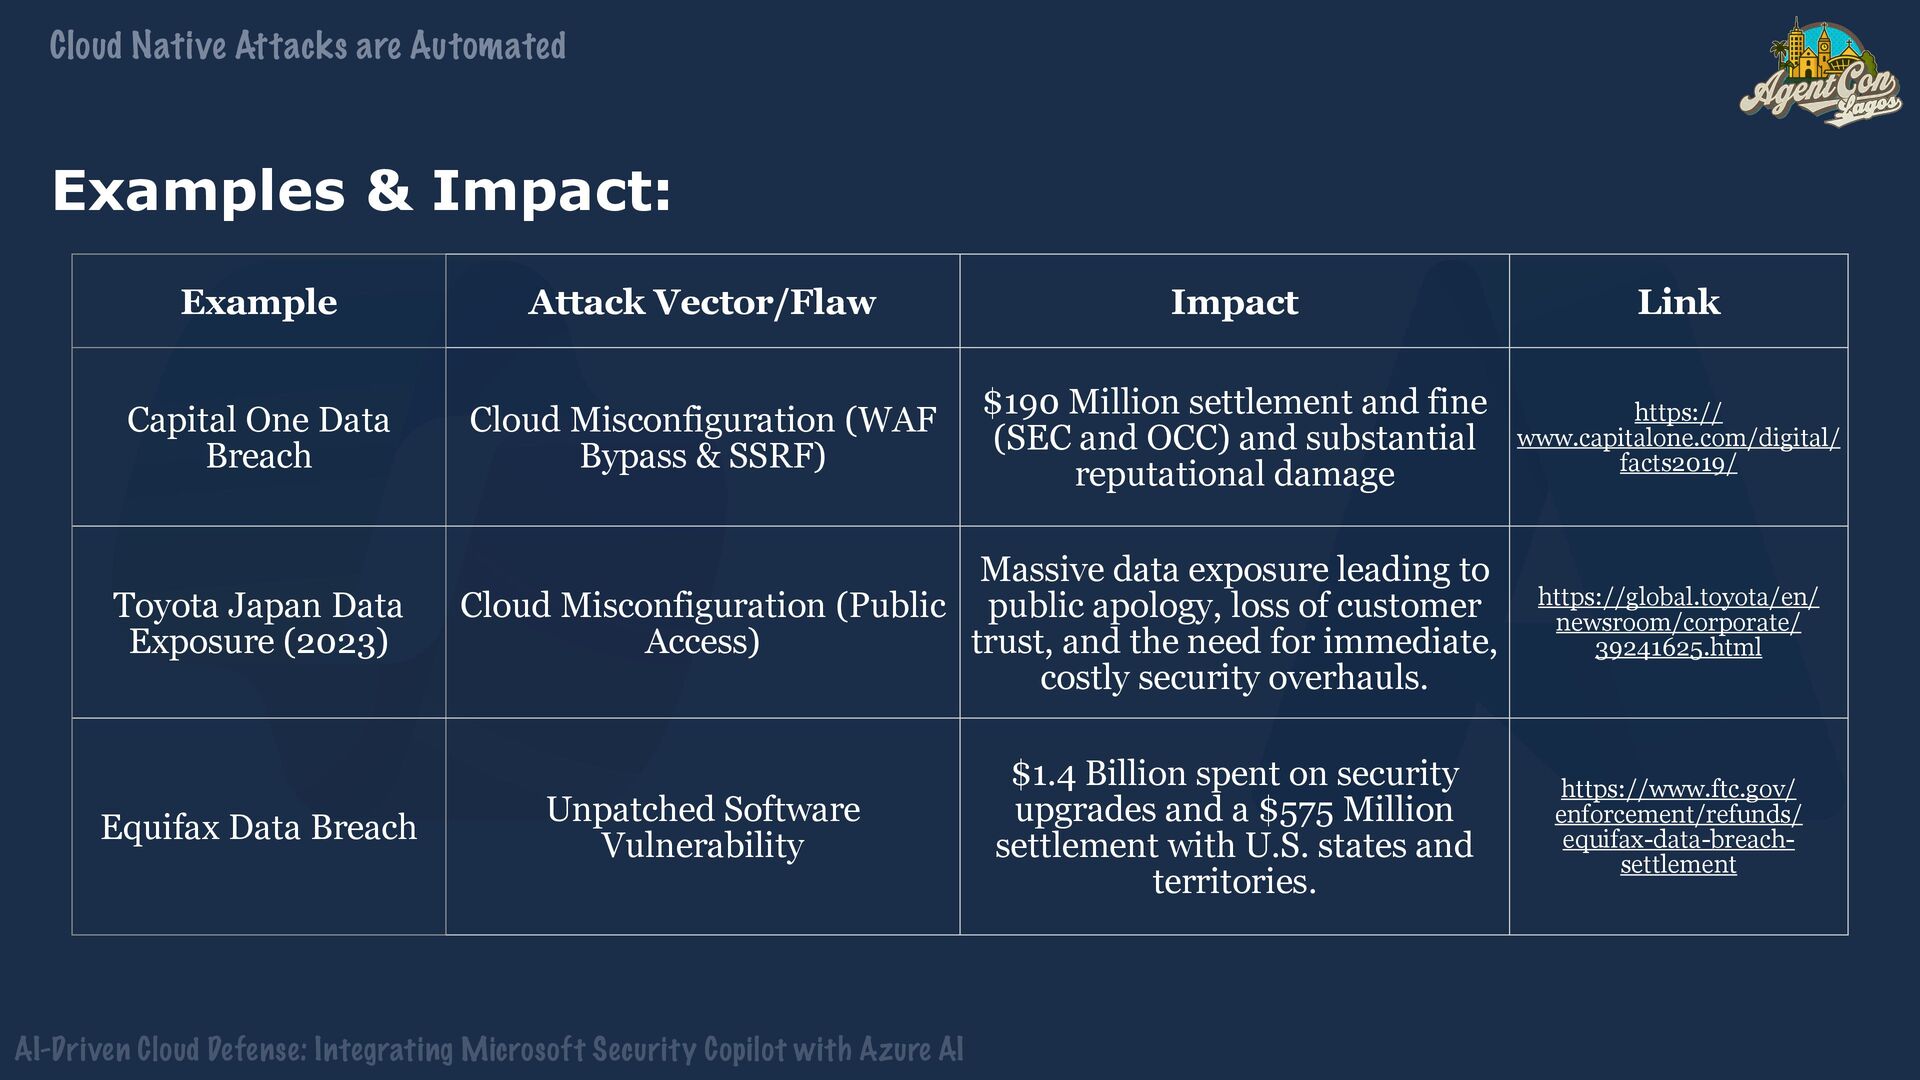
    AI Examples & Impact: Cloud Native Attacks are Automated Example Attack Vector/Flaw Impact Link Capital One Data Breach Cloud Misconfiguration (WAF Bypass & SSRF) $190 Million settlement and fine (SEC and OCC) and substantial reputational damage https:// www.capitalone.com/digital/ facts2019/ Toyota Japan Data Exposure (2023) Cloud Misconfiguration (Public Access) Massive data exposure leading to public apology, loss of customer trust, and the need for immediate, costly security overhauls. https://global.toyota/en/ newsroom/corporate/ 39241625.html Equifax Data Breach Unpatched Software Vulnerability $1.4 Billion spent on security upgrades and a $575 Million settlement with U.S. states and territories. https://www.ftc.gov/ enforcement/refunds/ equifax-data-breach- settlement
  4. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

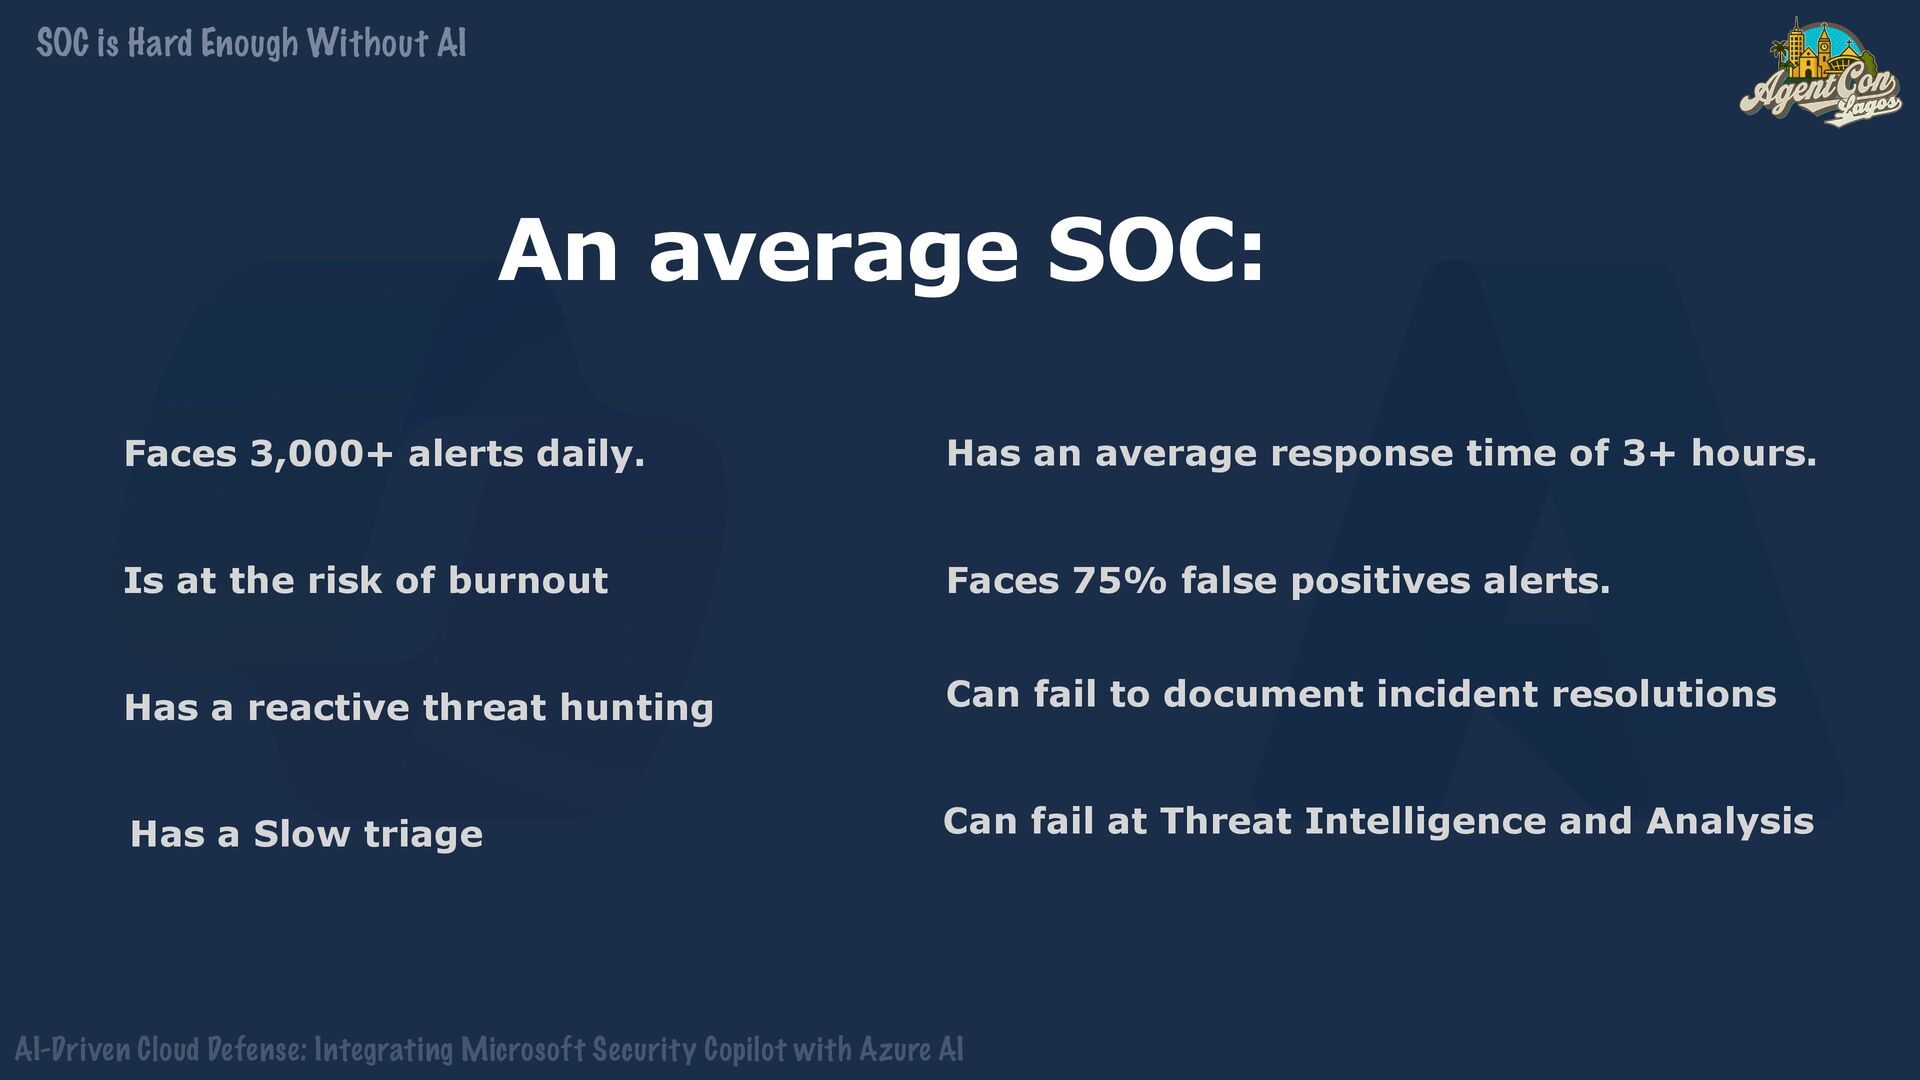
    AI SOC is Hard Enough Without AI An average SOC: Faces 3,000+ alerts daily. Has an average response time of 3+ hours. Faces 75% false positives alerts. Is at the risk of burnout Has a Slow triage Has a reactive threat hunting Can fail to document incident resolutions Can fail at Threat Intelligence and Analysis
  5. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

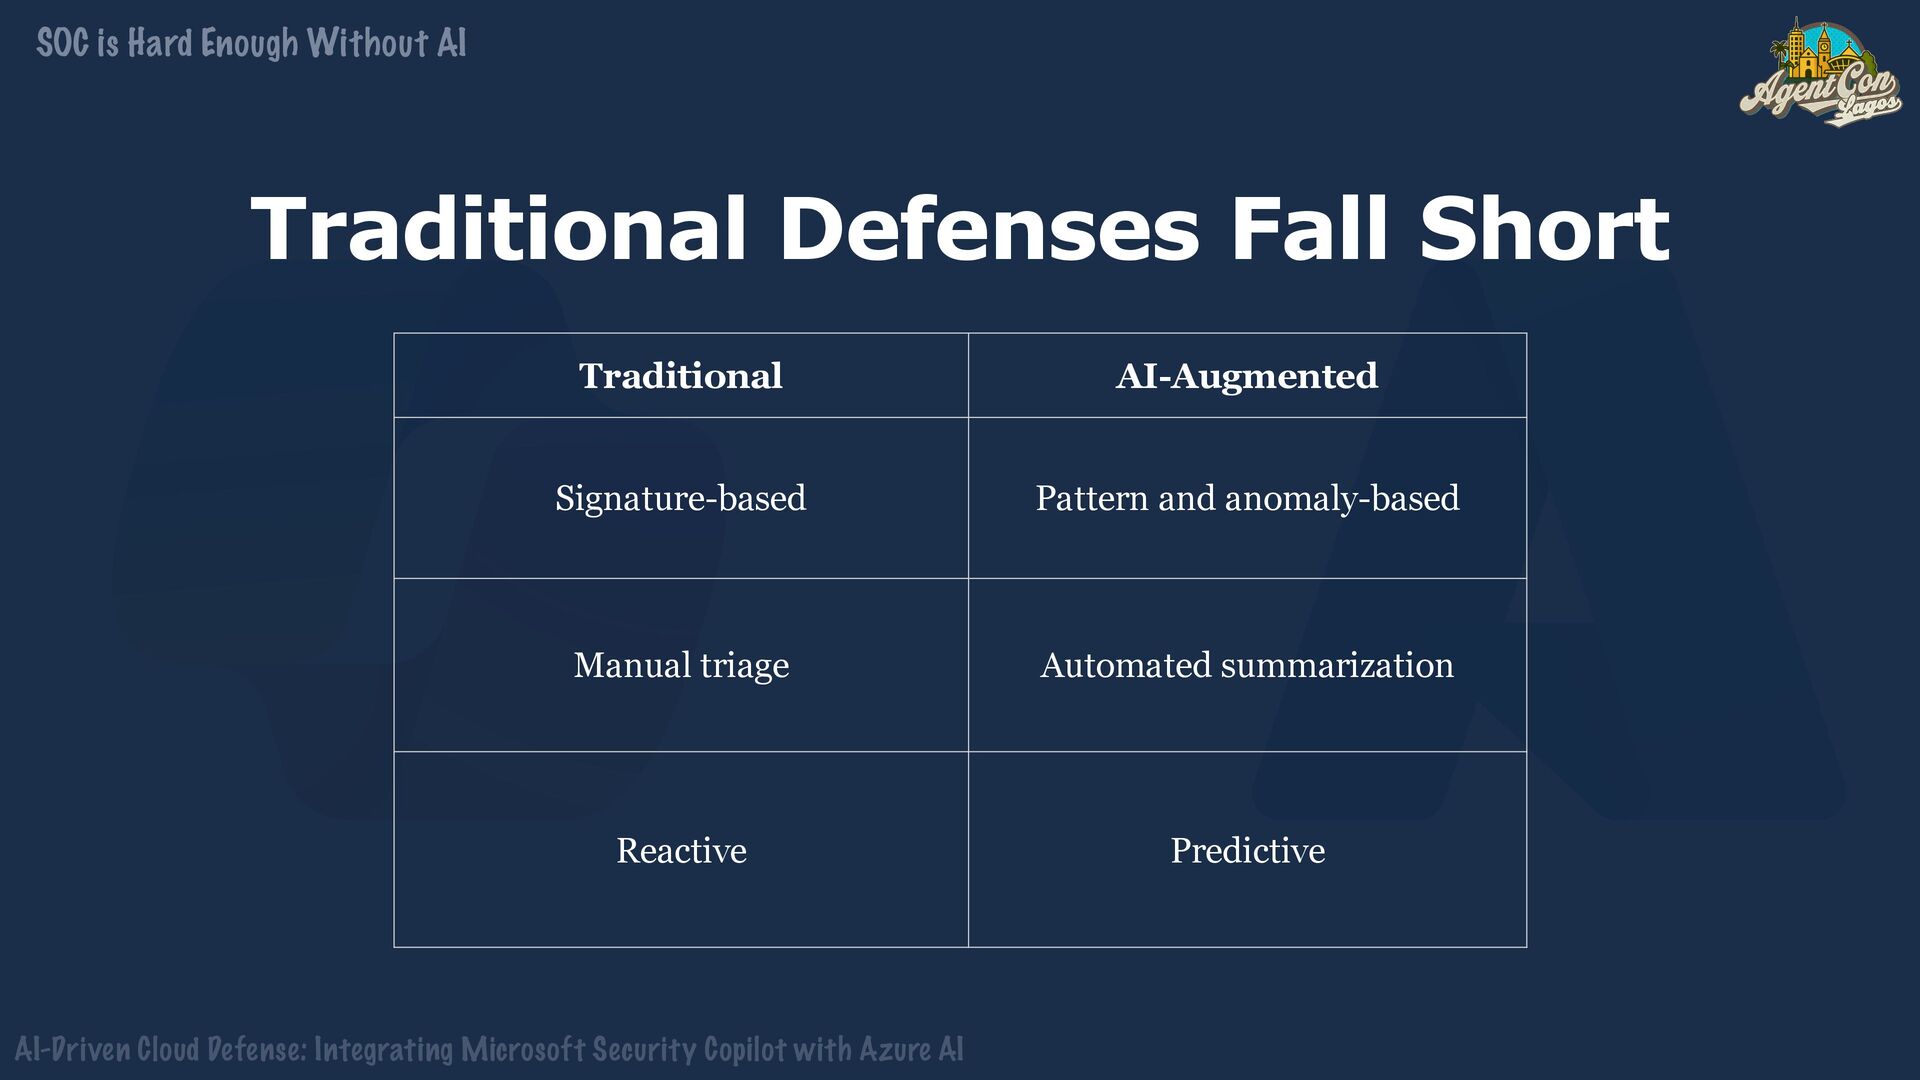
    AI SOC is Hard Enough Without AI Traditional Defenses Fall Short Traditional AI-Augmented Signature-based Pattern and anomaly-based Manual triage Automated summarization Reactive Predictive
  6. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

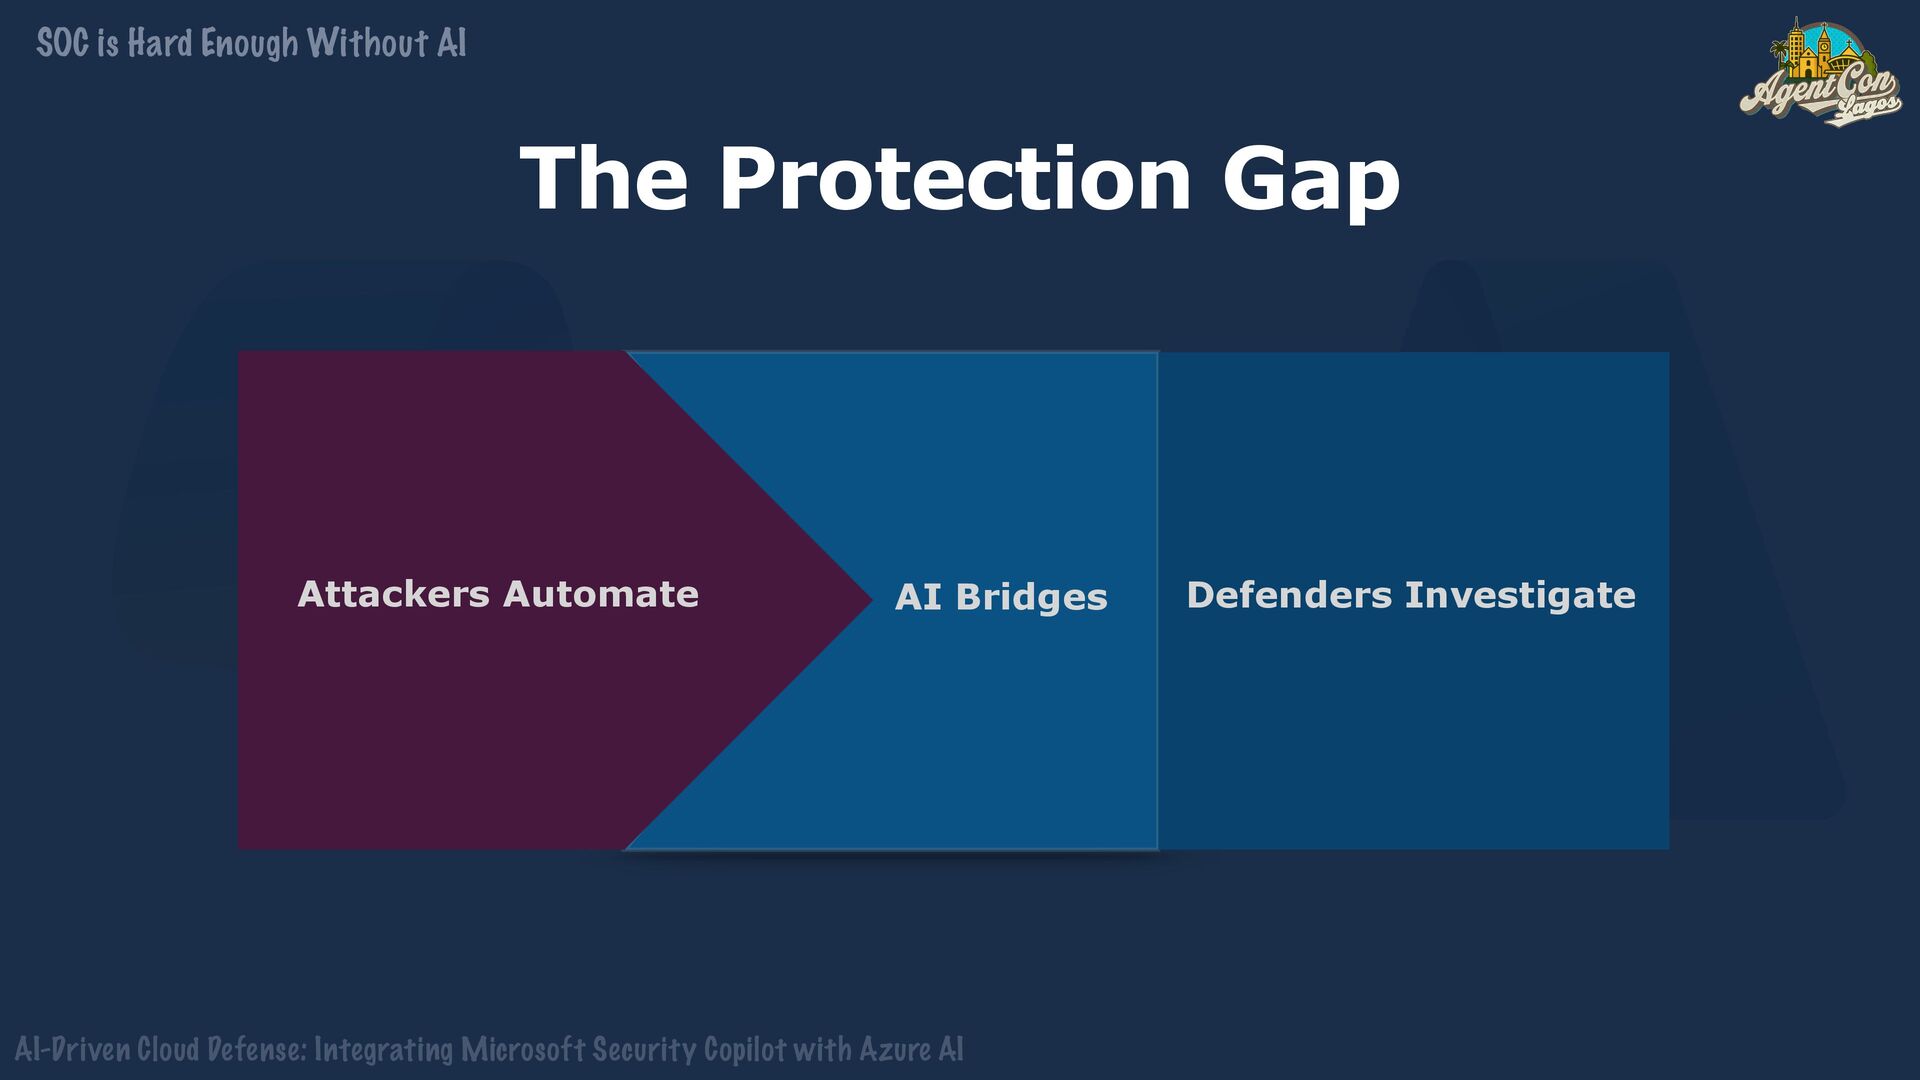
    AI SOC is Hard Enough Without AI The Protection Gap Attackers Automate AI Bridges Defenders Investigate
  7. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Traditional SOC Workflow SOC is Hard Enough Without AI
  8. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Attackers only need gap! SOC is Hard Enough Without AI Defenders must cover all. defense must be automated the same way attack is!
  9. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Microsoft Security Copilot! Introducing… Built on Microsoft’s OpenAI Service. Combines GPT intelligence with Microsoft threat data. Integrates natively with Defender XDR, Sentinel, Intune.
  10. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Microsoft Security Copilot! Incident summarization KQL query generation Threat correlation Copilot Capabilities Guided investigation and recommendations correlation
  11. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

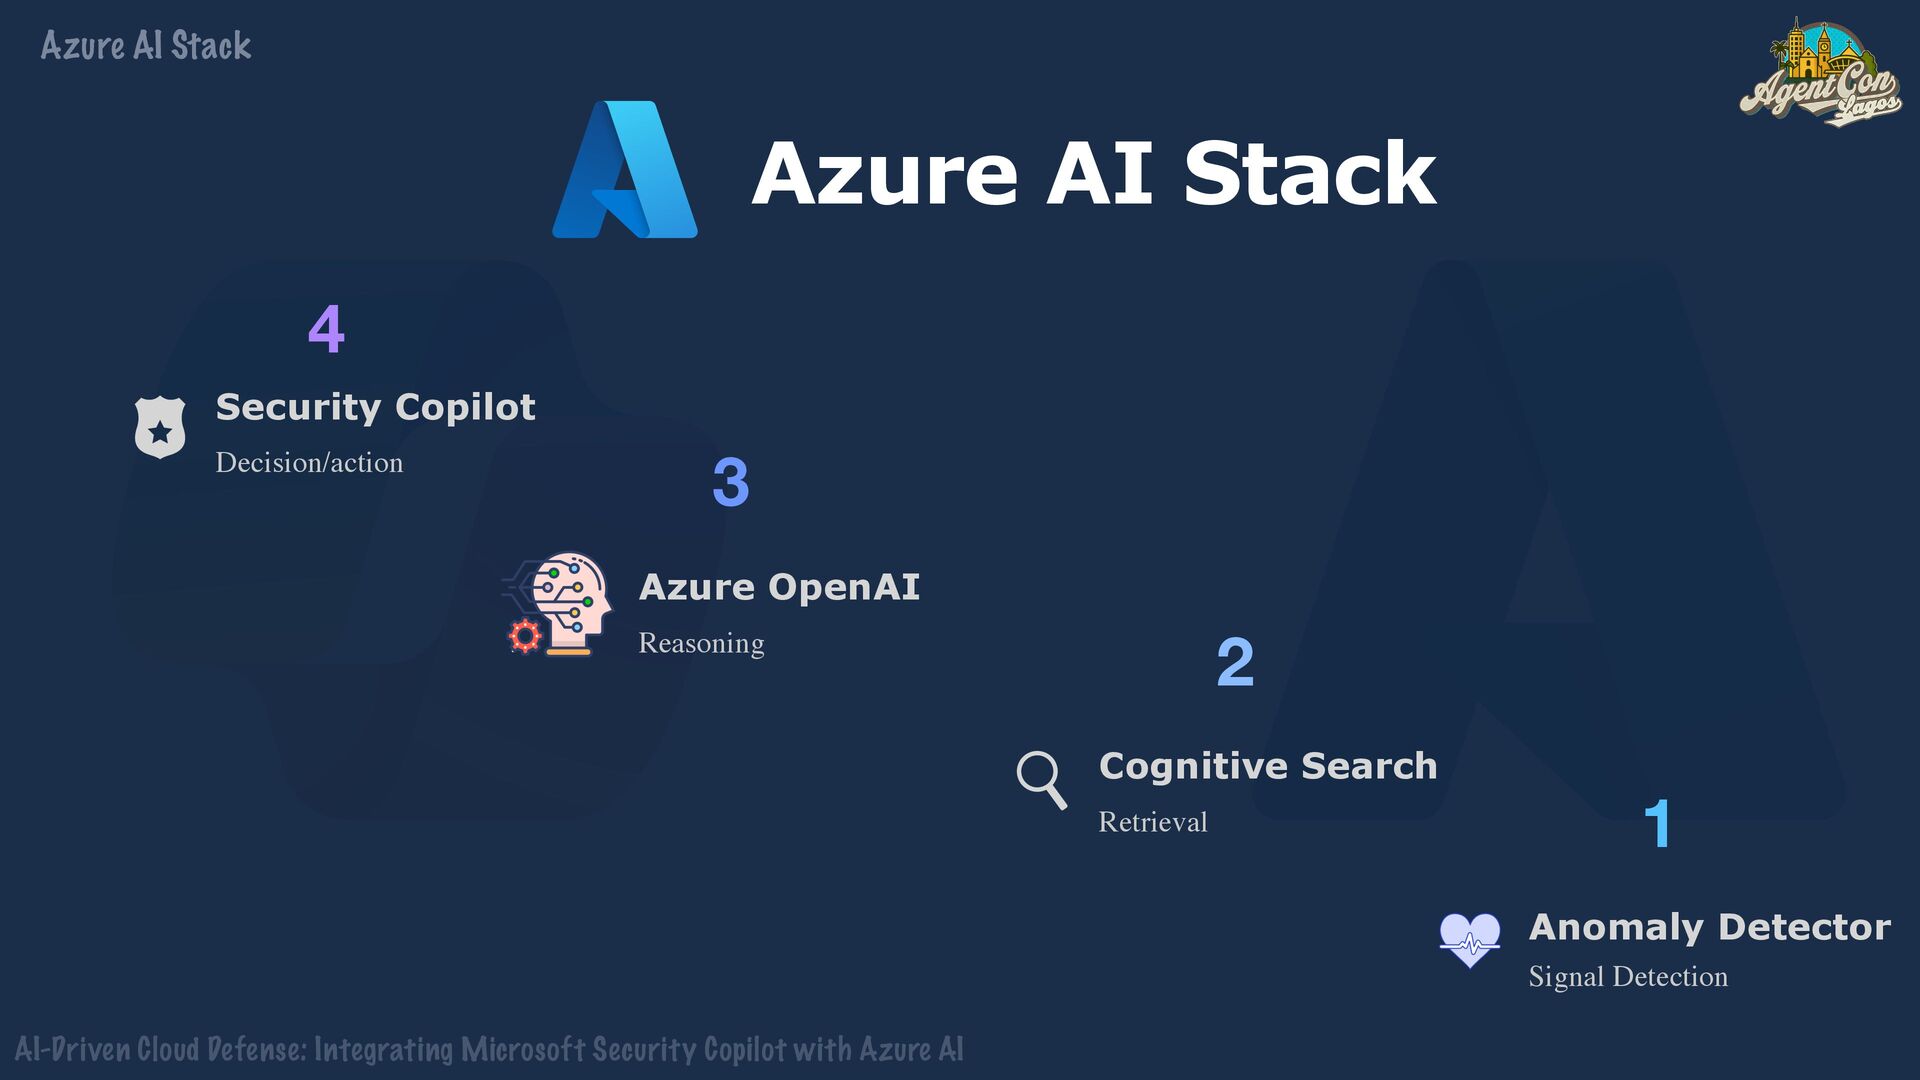
    AI Azure AI Stack Anomaly Detector Azure AI Stack Signal Detection Cognitive Search Retrieval Azure OpenAI Reasoning Security Copilot Decision/action 1 2 3 4
  12. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

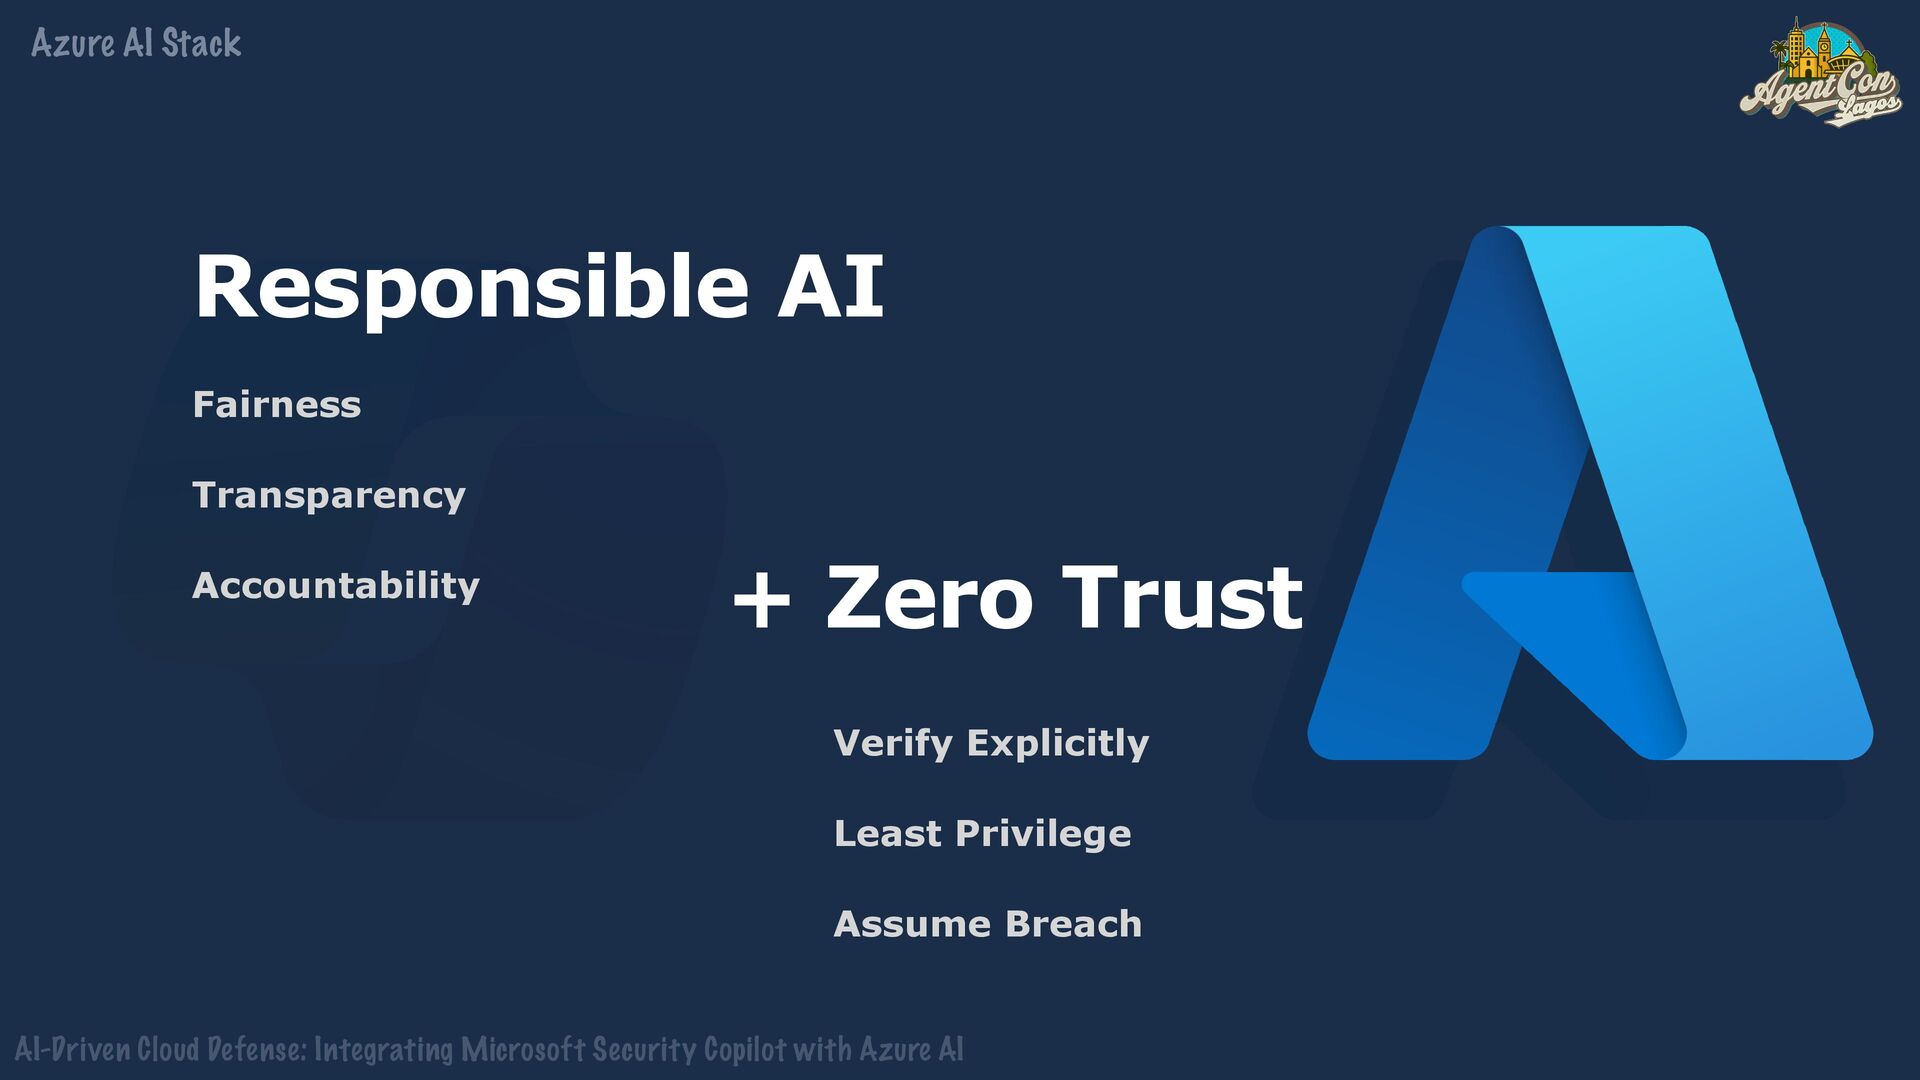
    AI Azure AI Stack + Zero Trust Verify Explicitly Least Privilege Assume Breach Fairness Transparency Accountability Responsible AI
  13. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

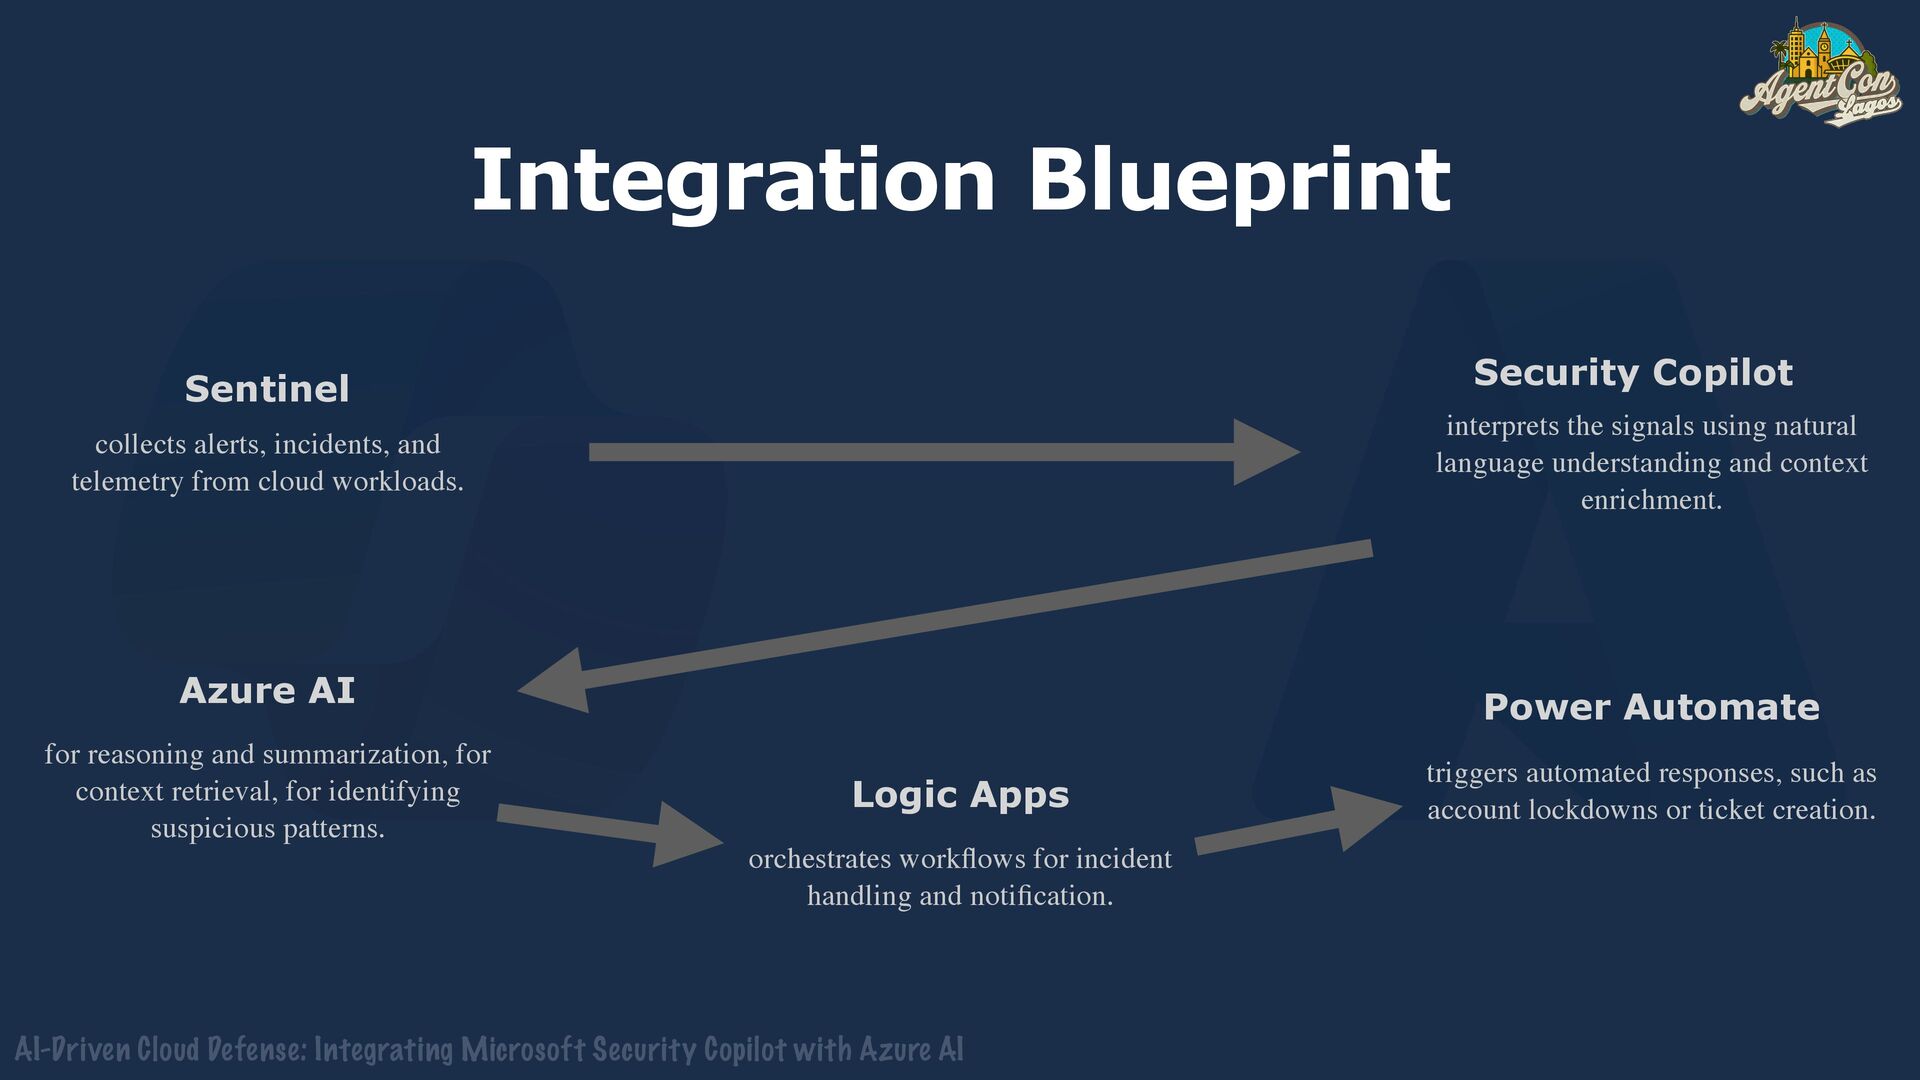
    AI Integration Blueprint Sentinel collects alerts, incidents, and telemetry from cloud workloads. Security Copilot interprets the signals using natural language understanding and context enrichment. Azure AI for reasoning and summarization, for context retrieval, for identifying suspicious patterns. Logic Apps orchestrates work fl ows for incident handling and noti fi cation. Power Automate triggers automated responses, such as account lockdowns or ticket creation.
  14. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

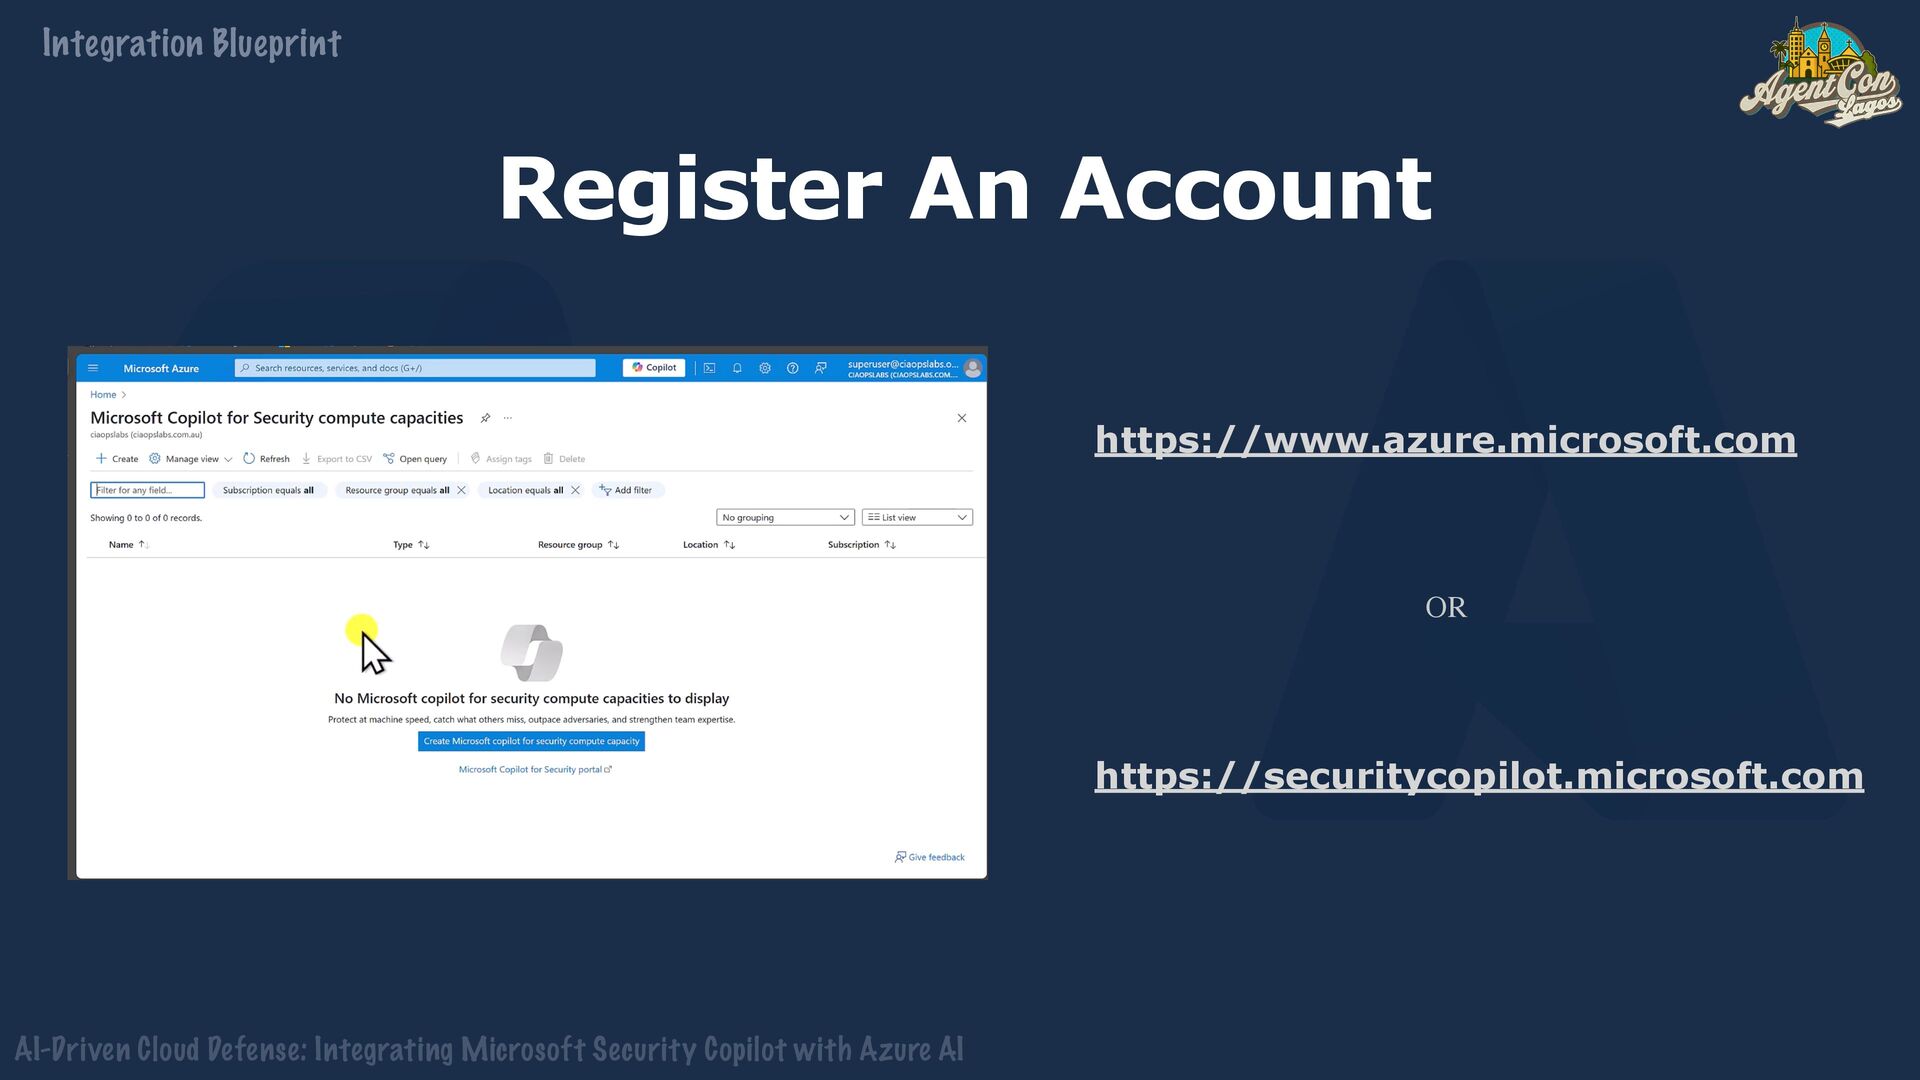
    AI Integration Blueprint Register An Account https://www.azure.microsoft.com https://securitycopilot.microsoft.com OR
  15. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

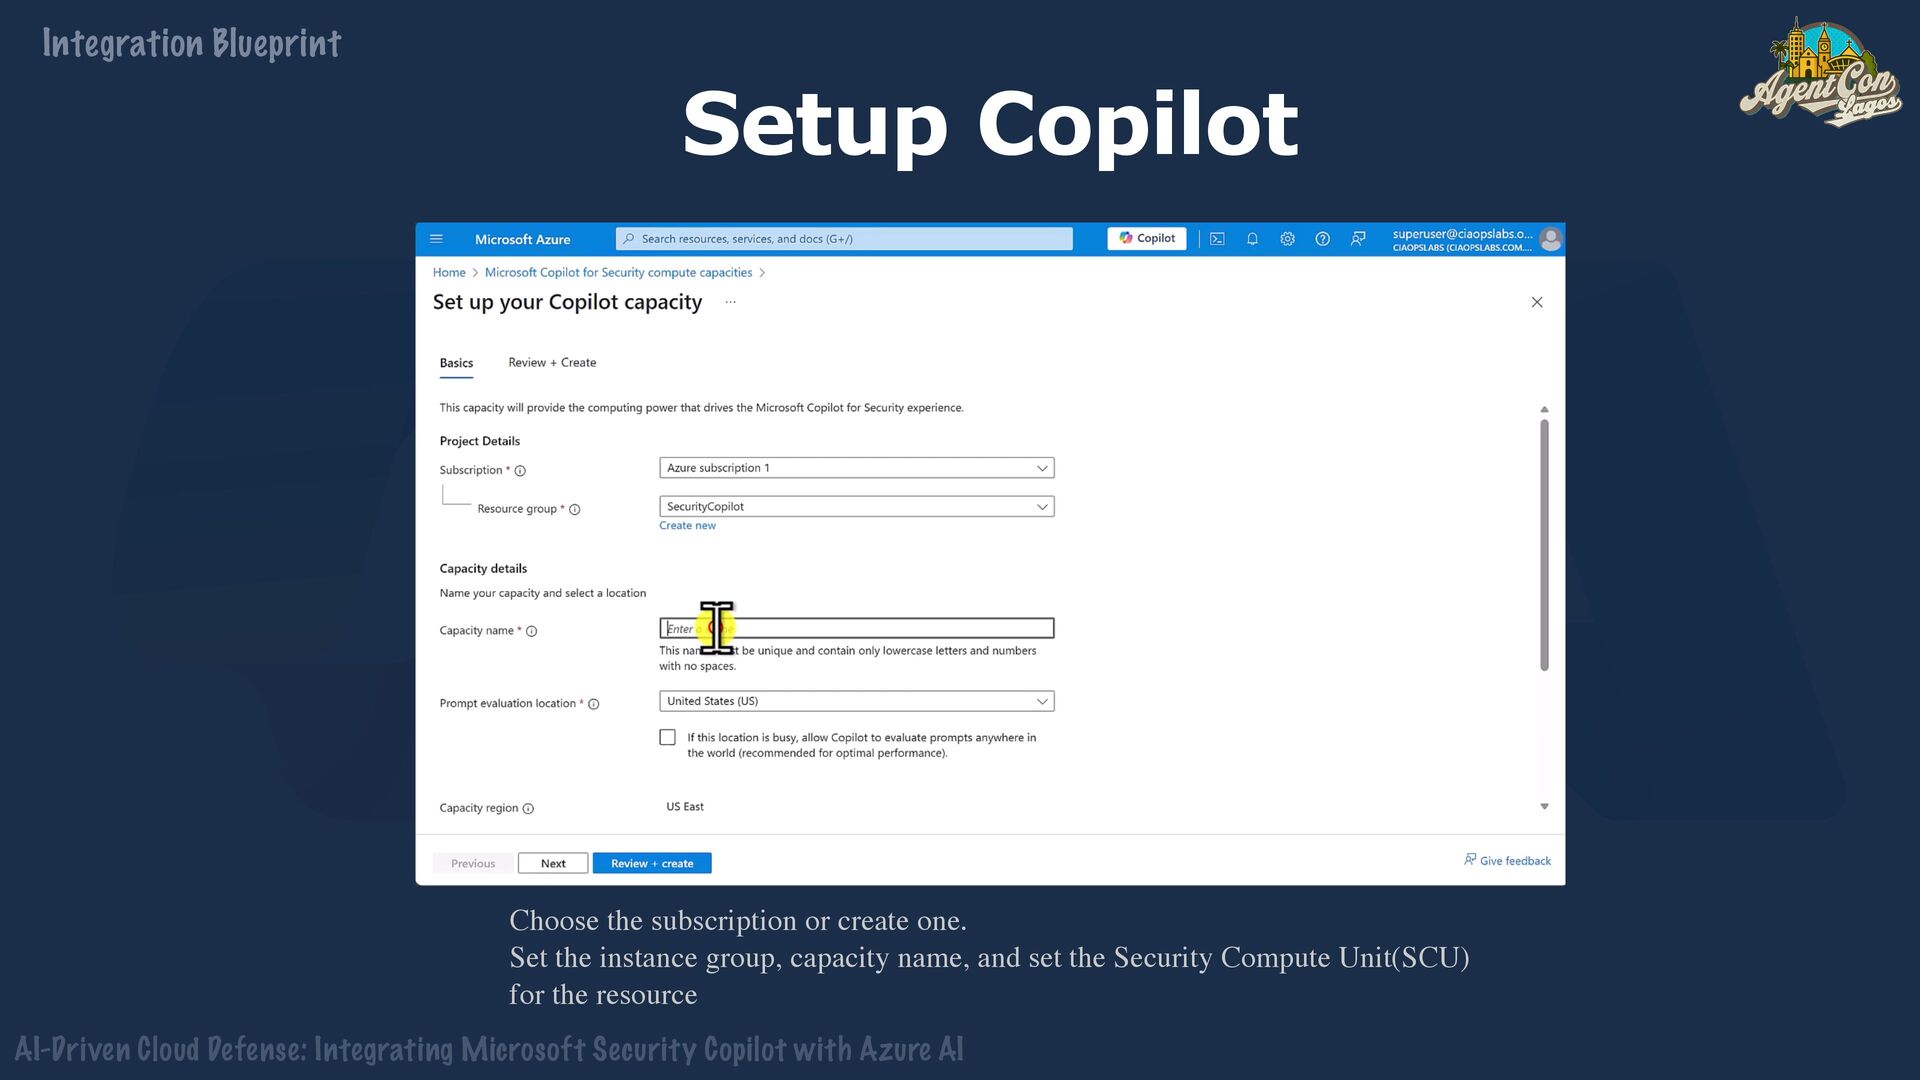
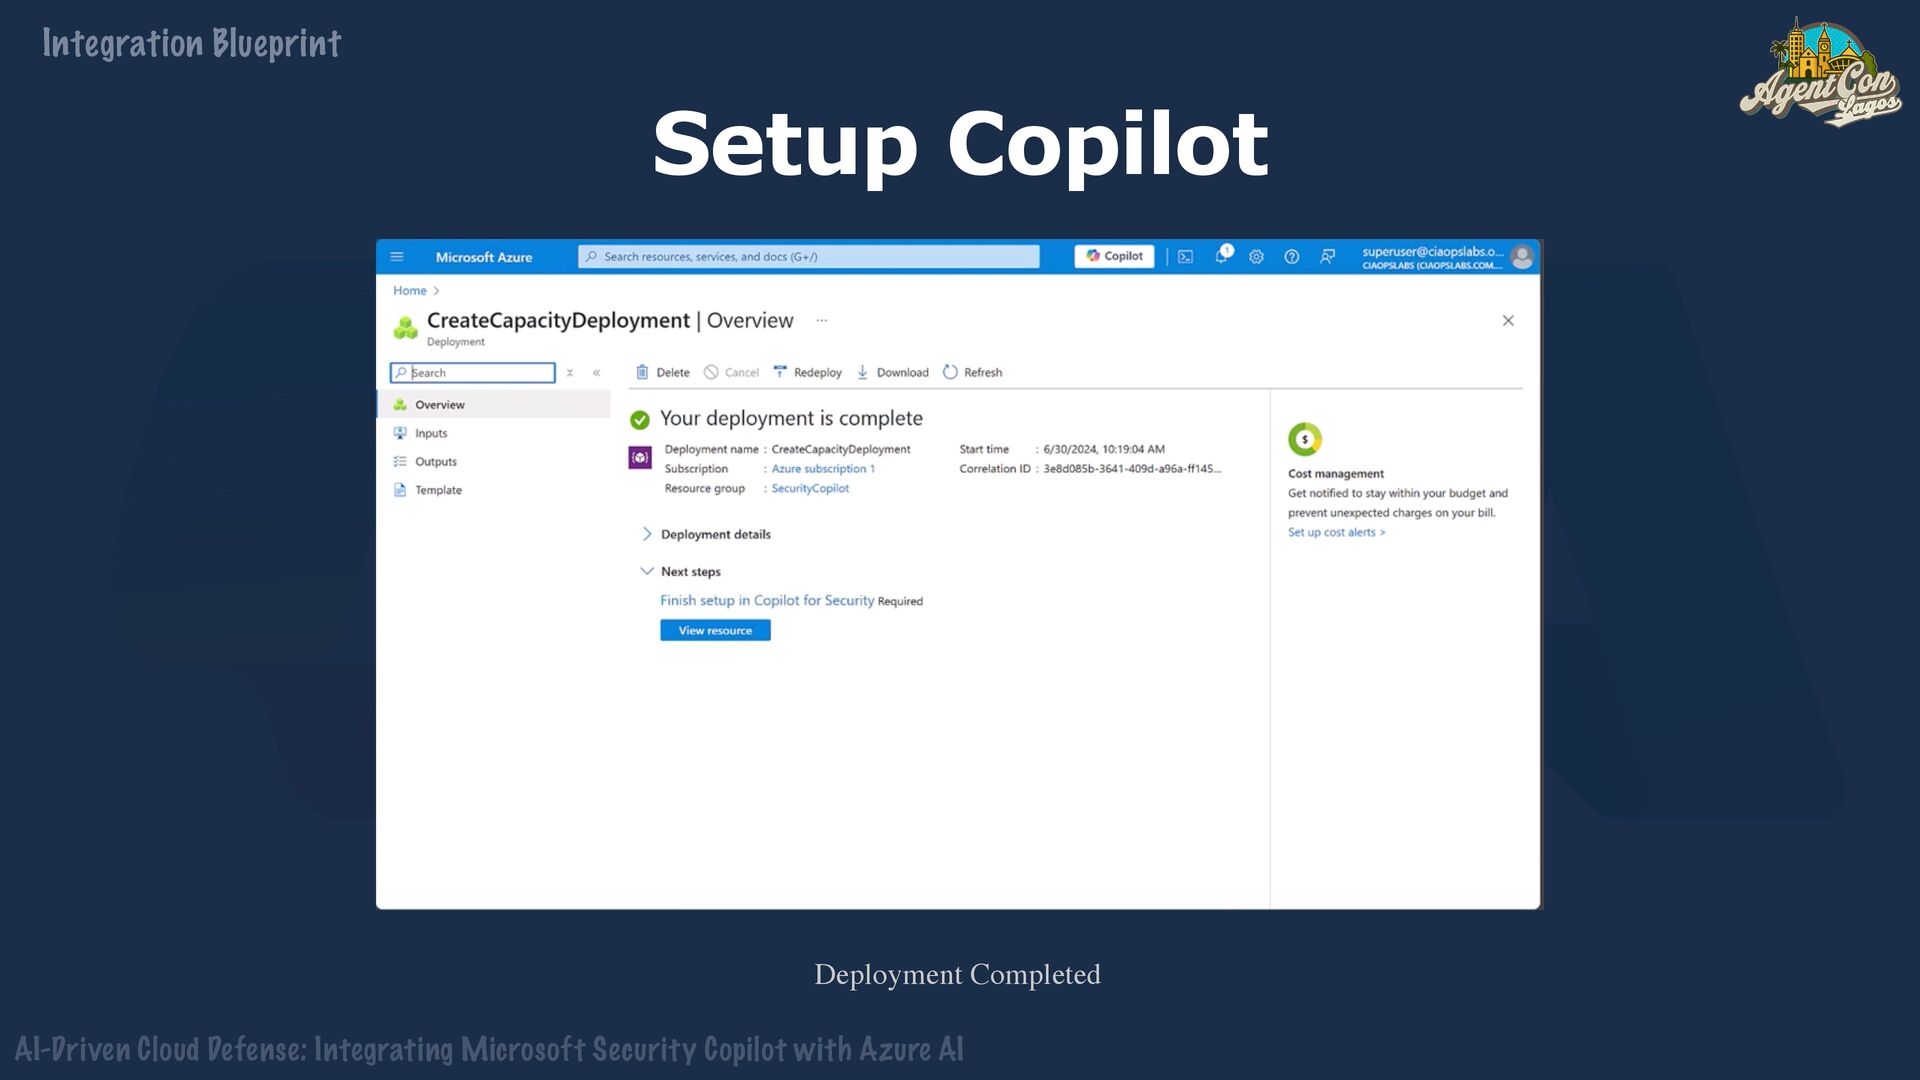
    AI Integration Blueprint Setup Copilot Choose the subscription or create one. Set the instance group, capacity name, and set the Security Compute Unit(SCU) for the resource
  16. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

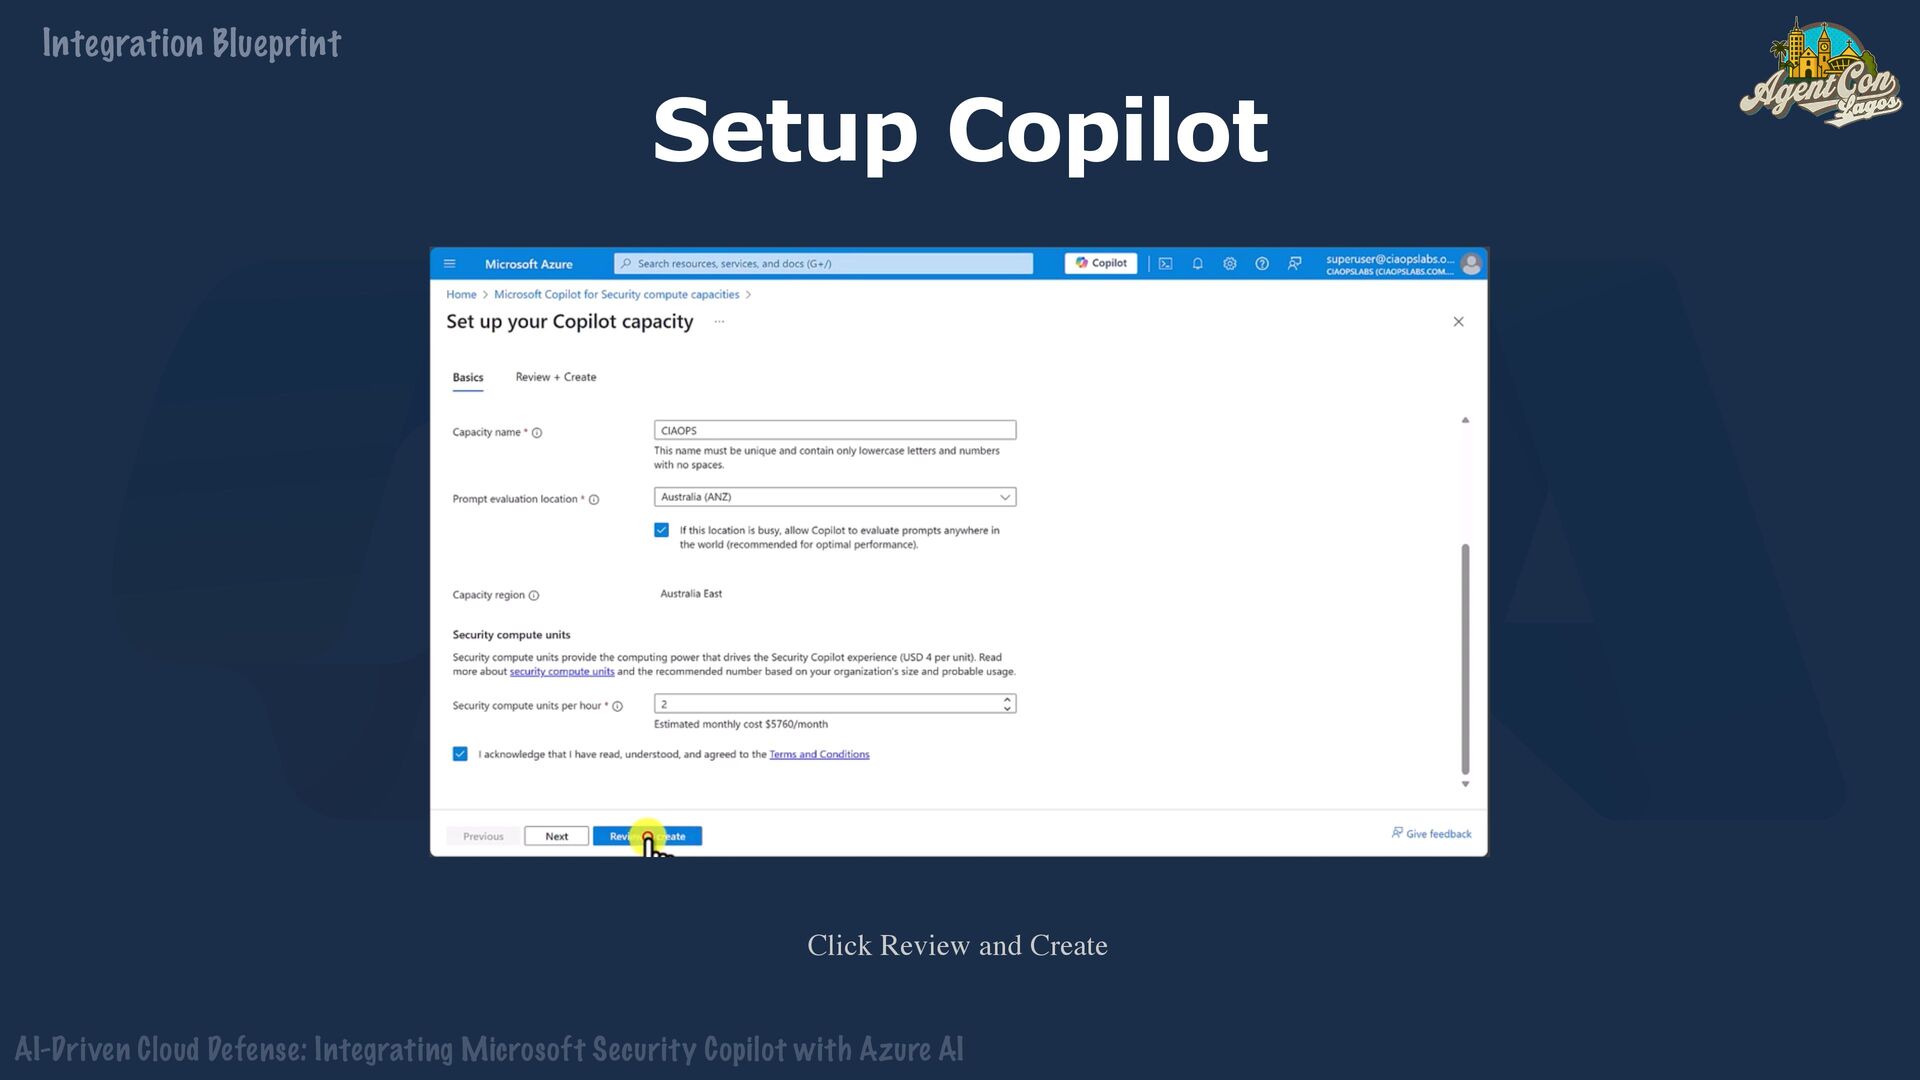
    AI Setup Copilot Click Review and Create Integration Blueprint
  17. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

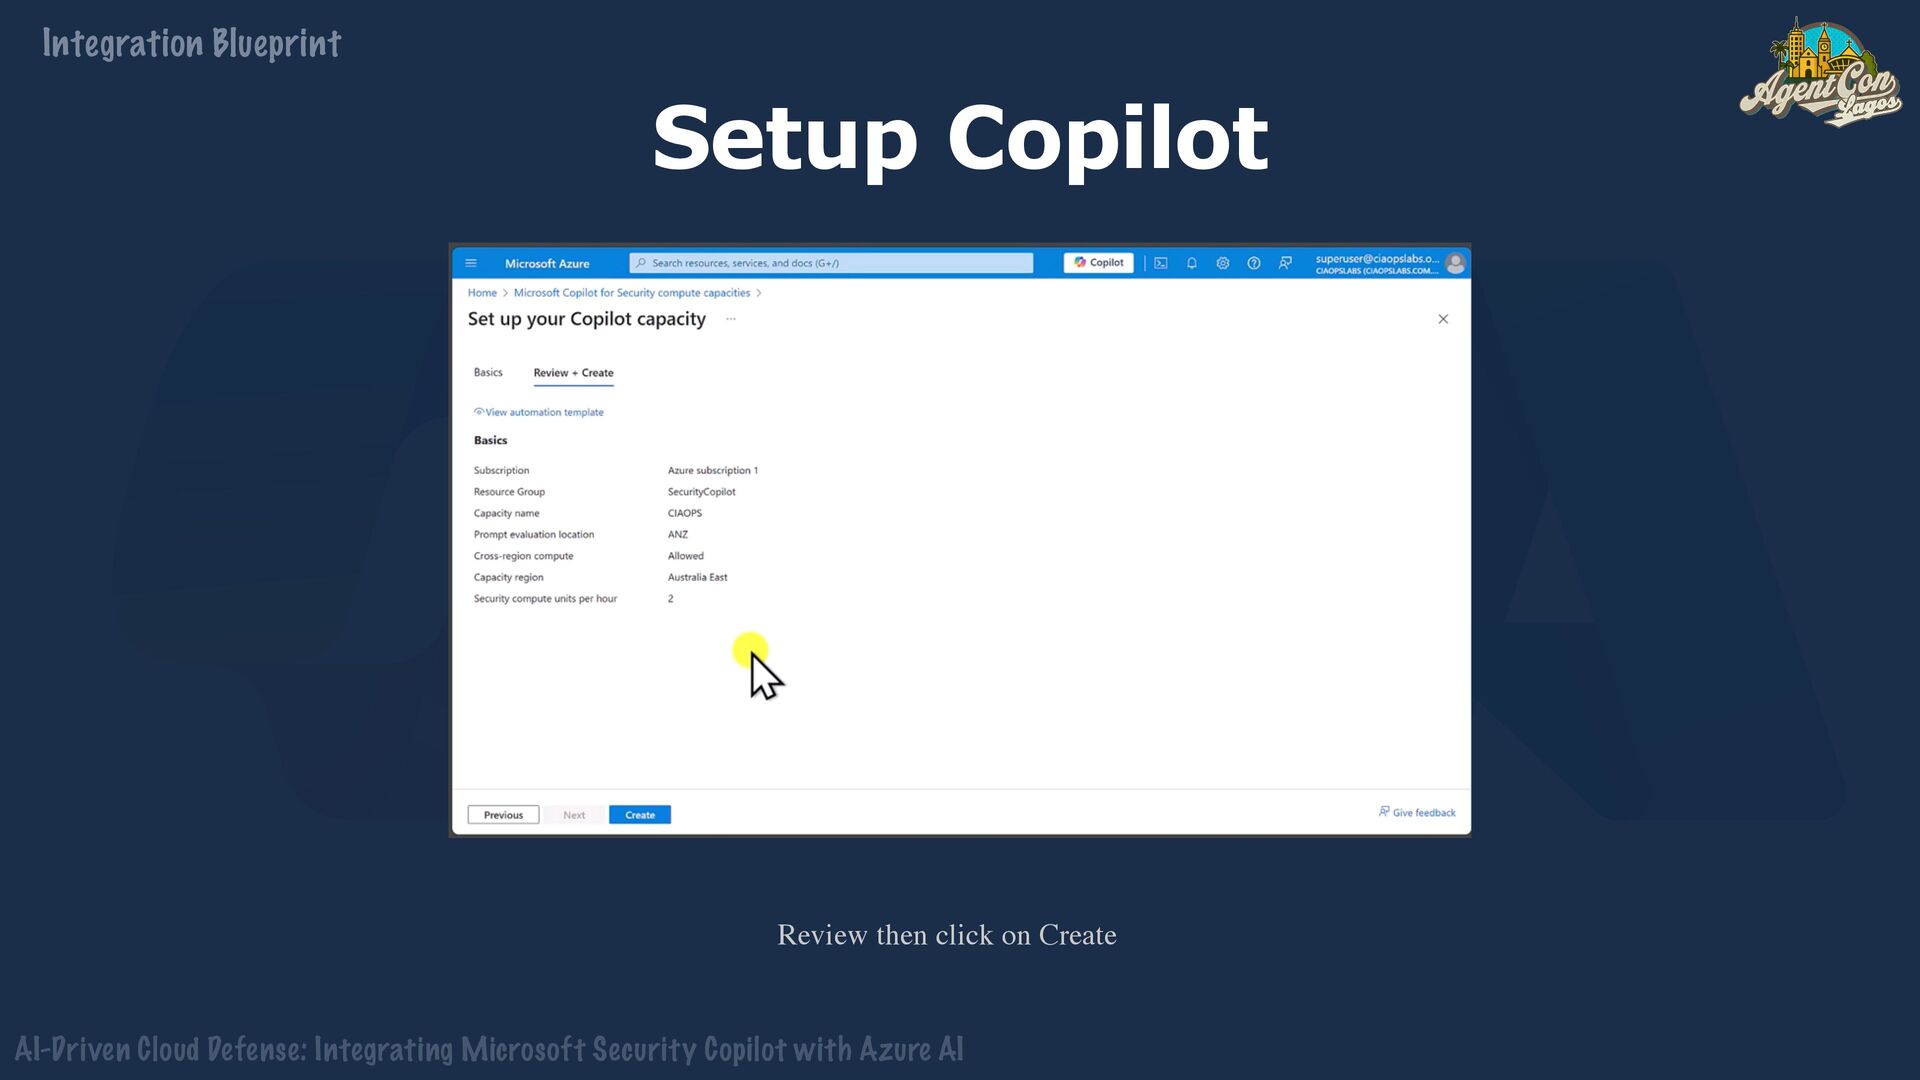
    AI Setup Copilot Integration Blueprint Review then click on Create
  18. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Setup Copilot Integration Blueprint Deployment Completed
  19. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

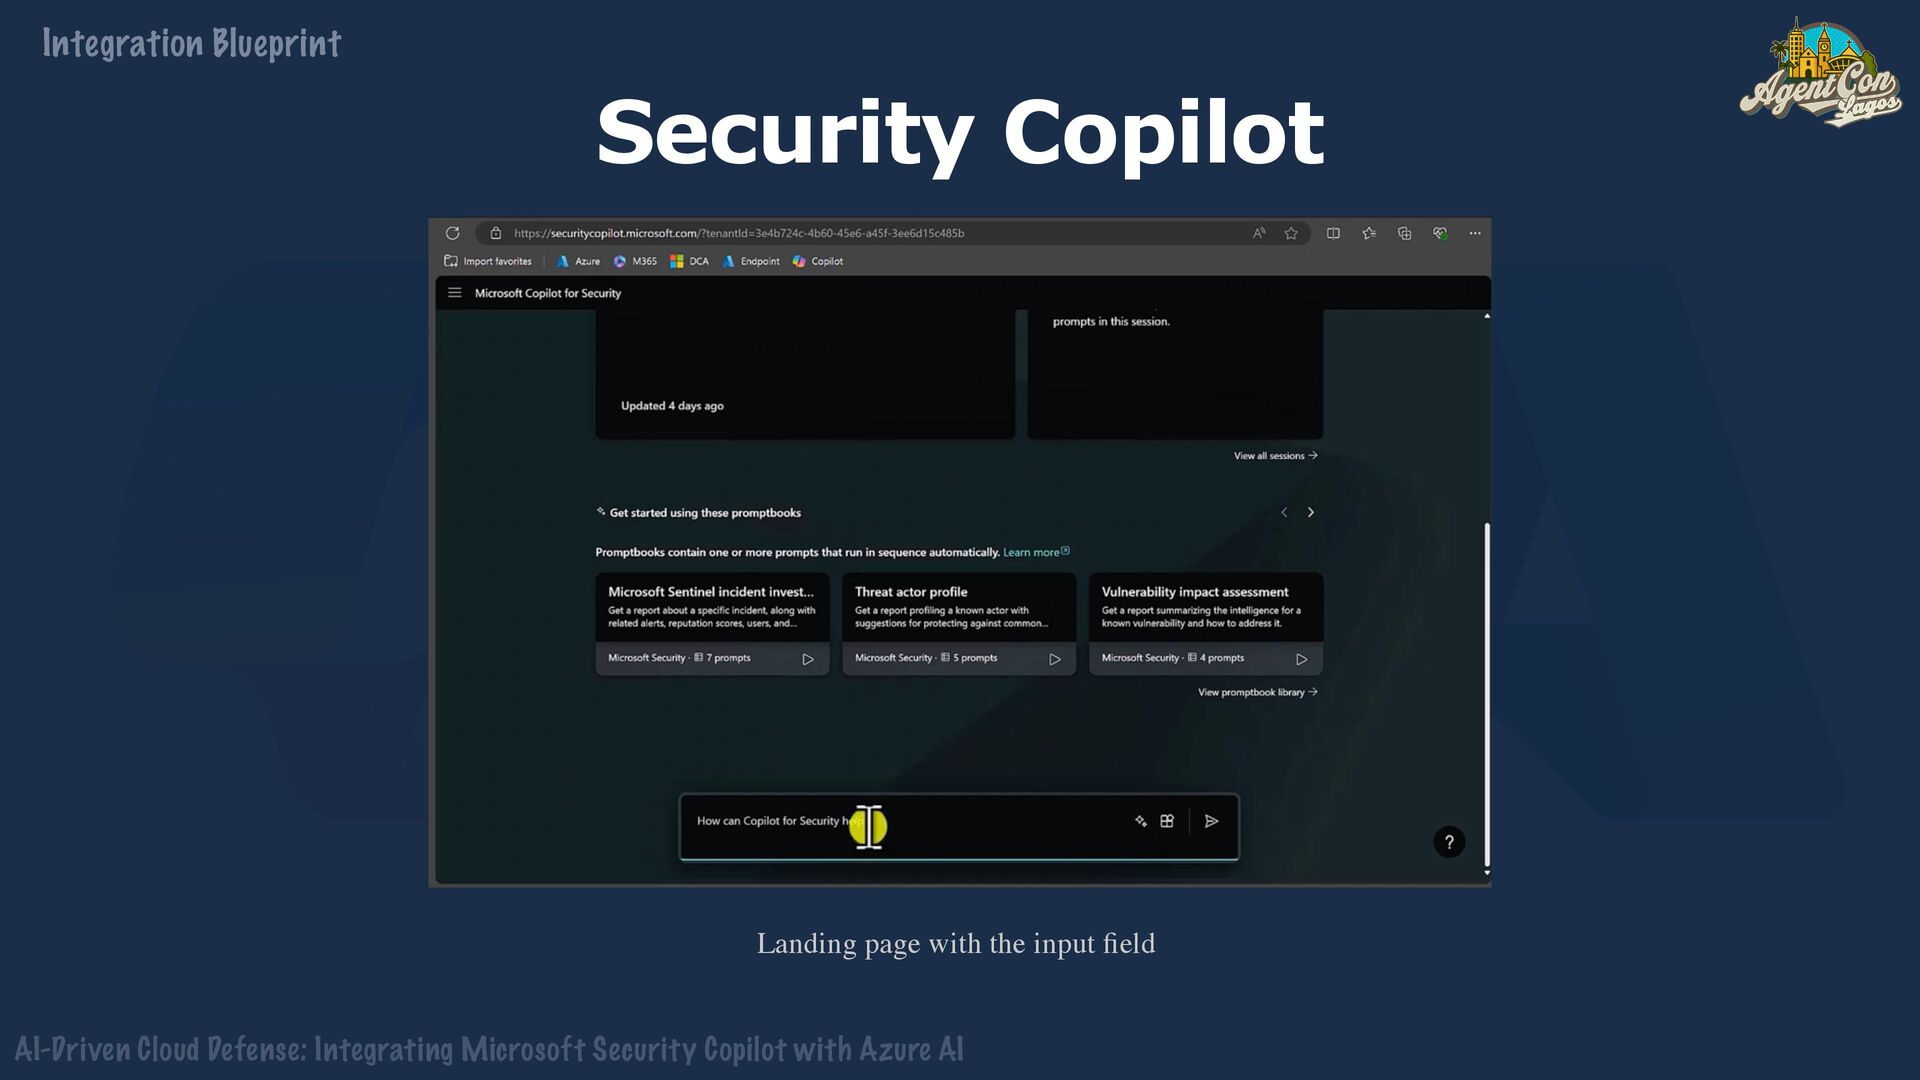
    AI Security Copilot Integration Blueprint Landing page with the input fi eld
  20. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

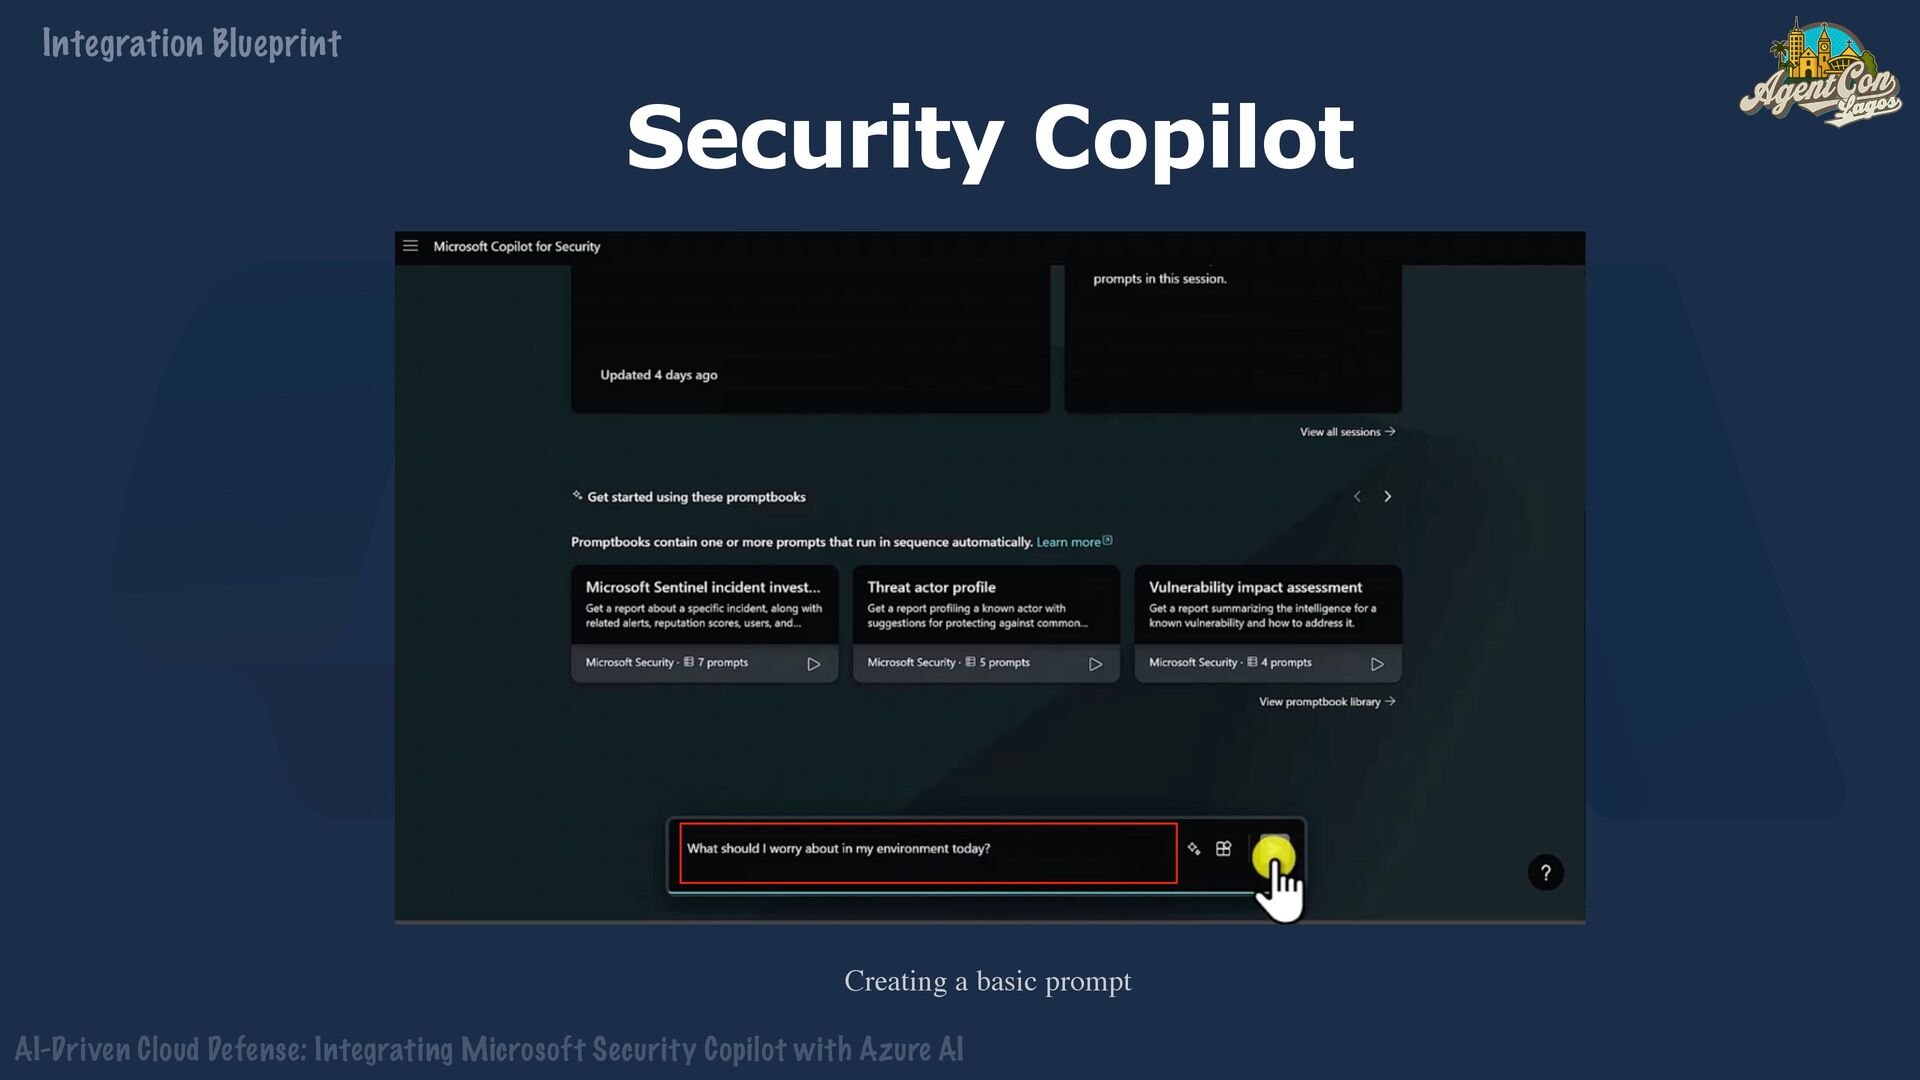
    AI Security Copilot Integration Blueprint Creating a basic prompt
  21. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

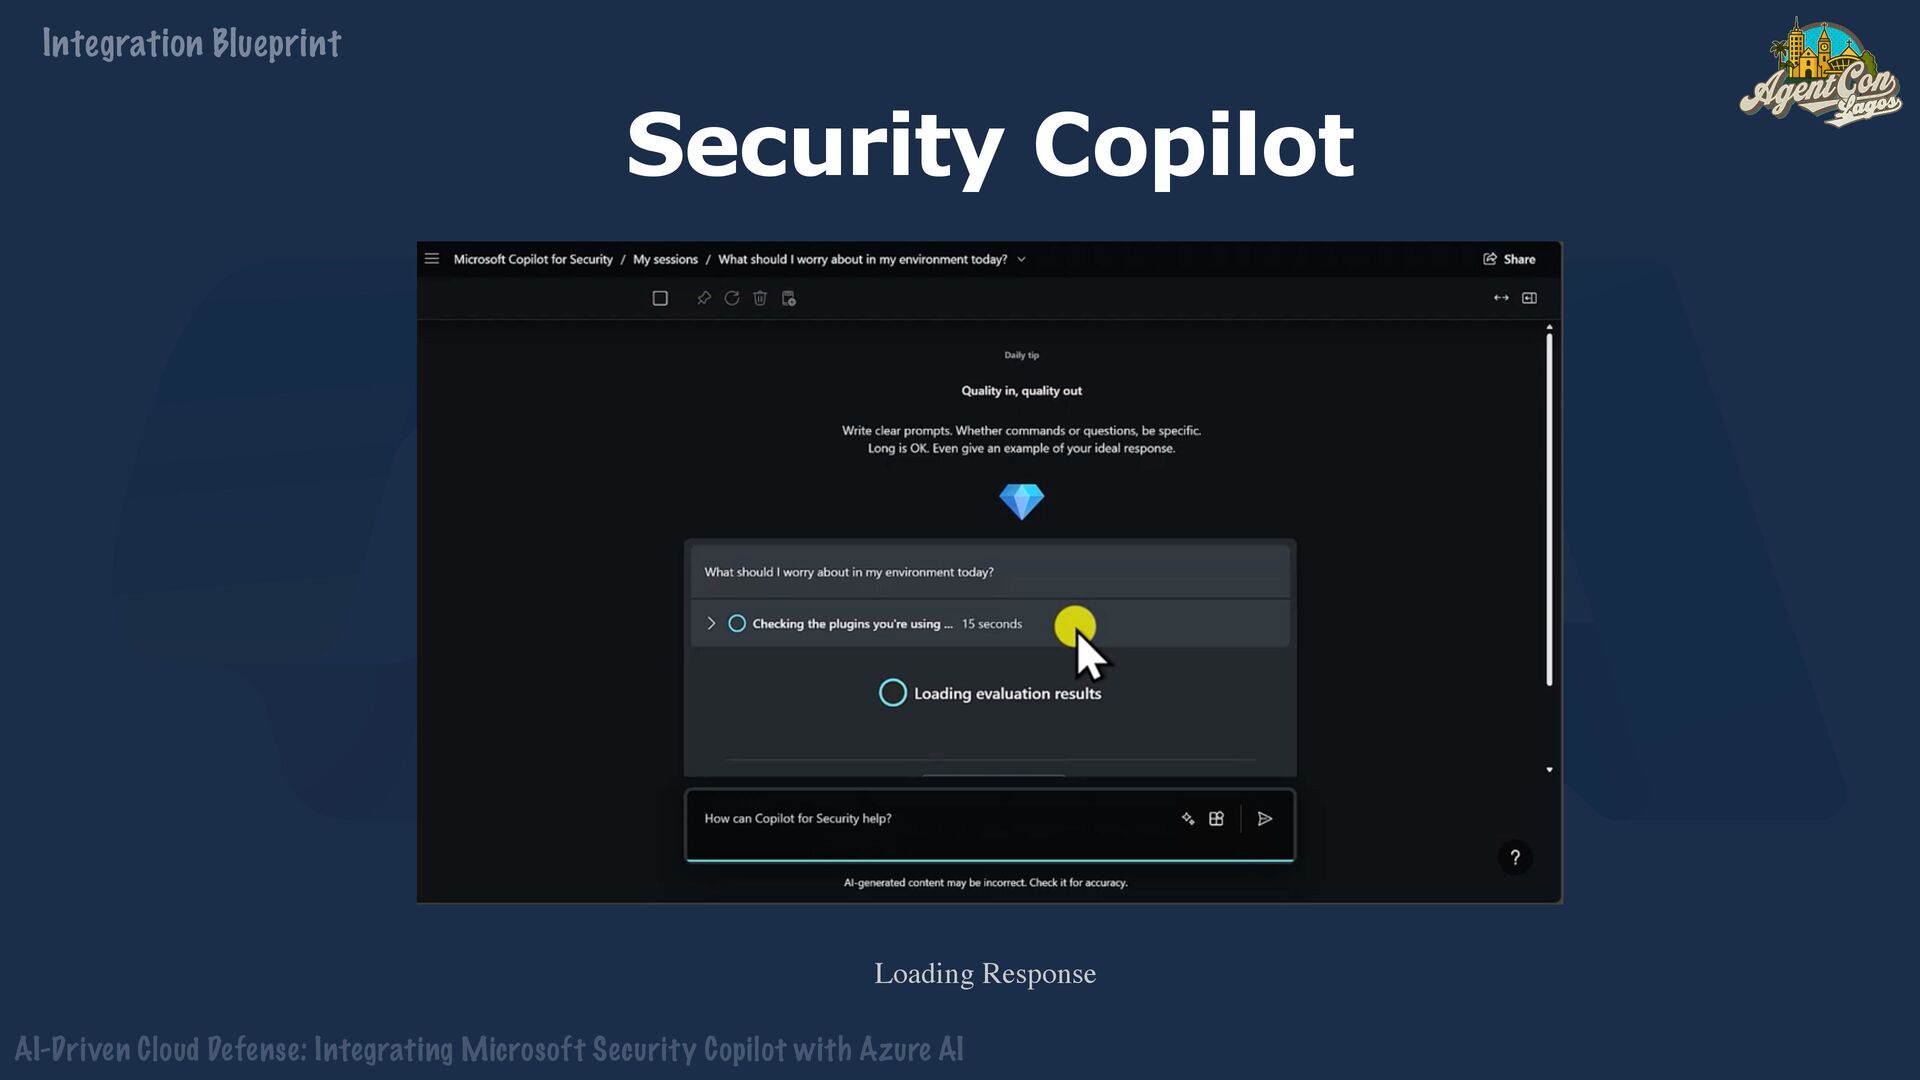
    AI Security Copilot Integration Blueprint Loading Response
  22. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

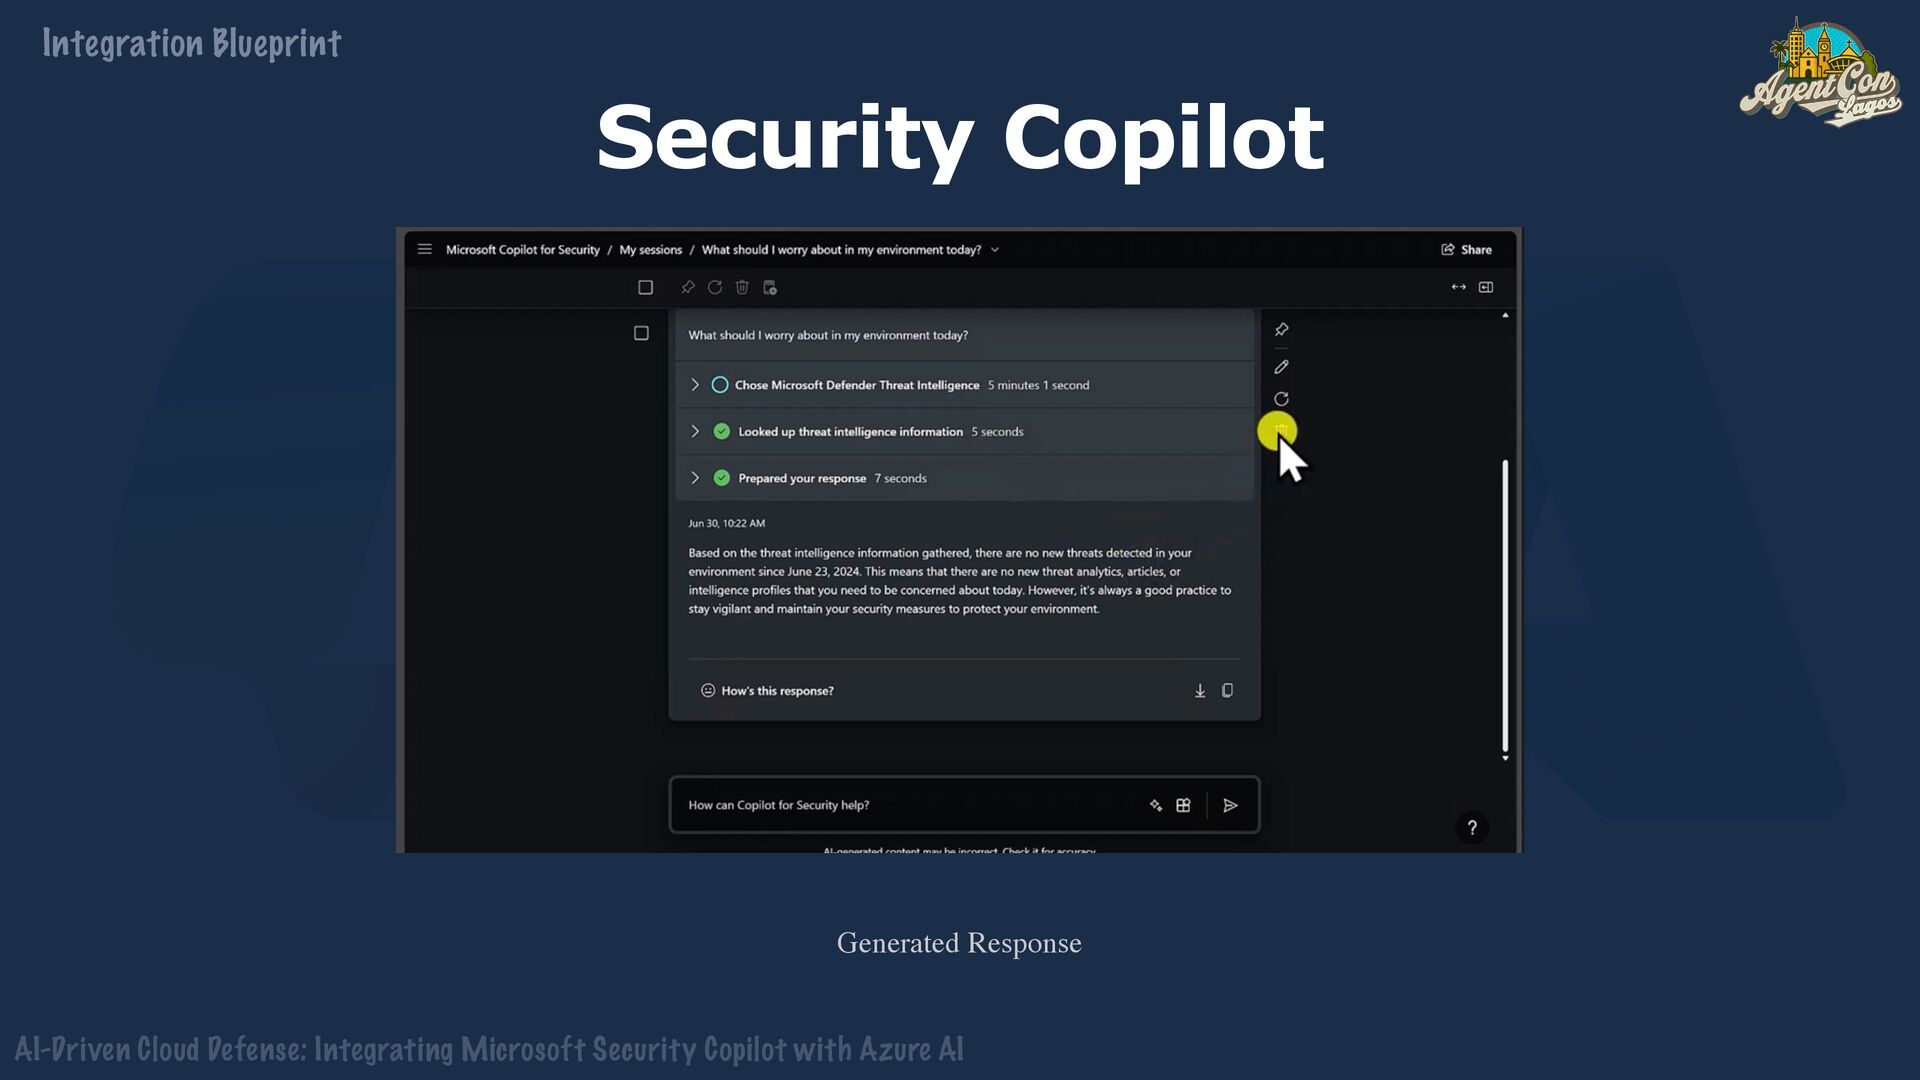
    AI Security Copilot Integration Blueprint Generated Response
  23. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

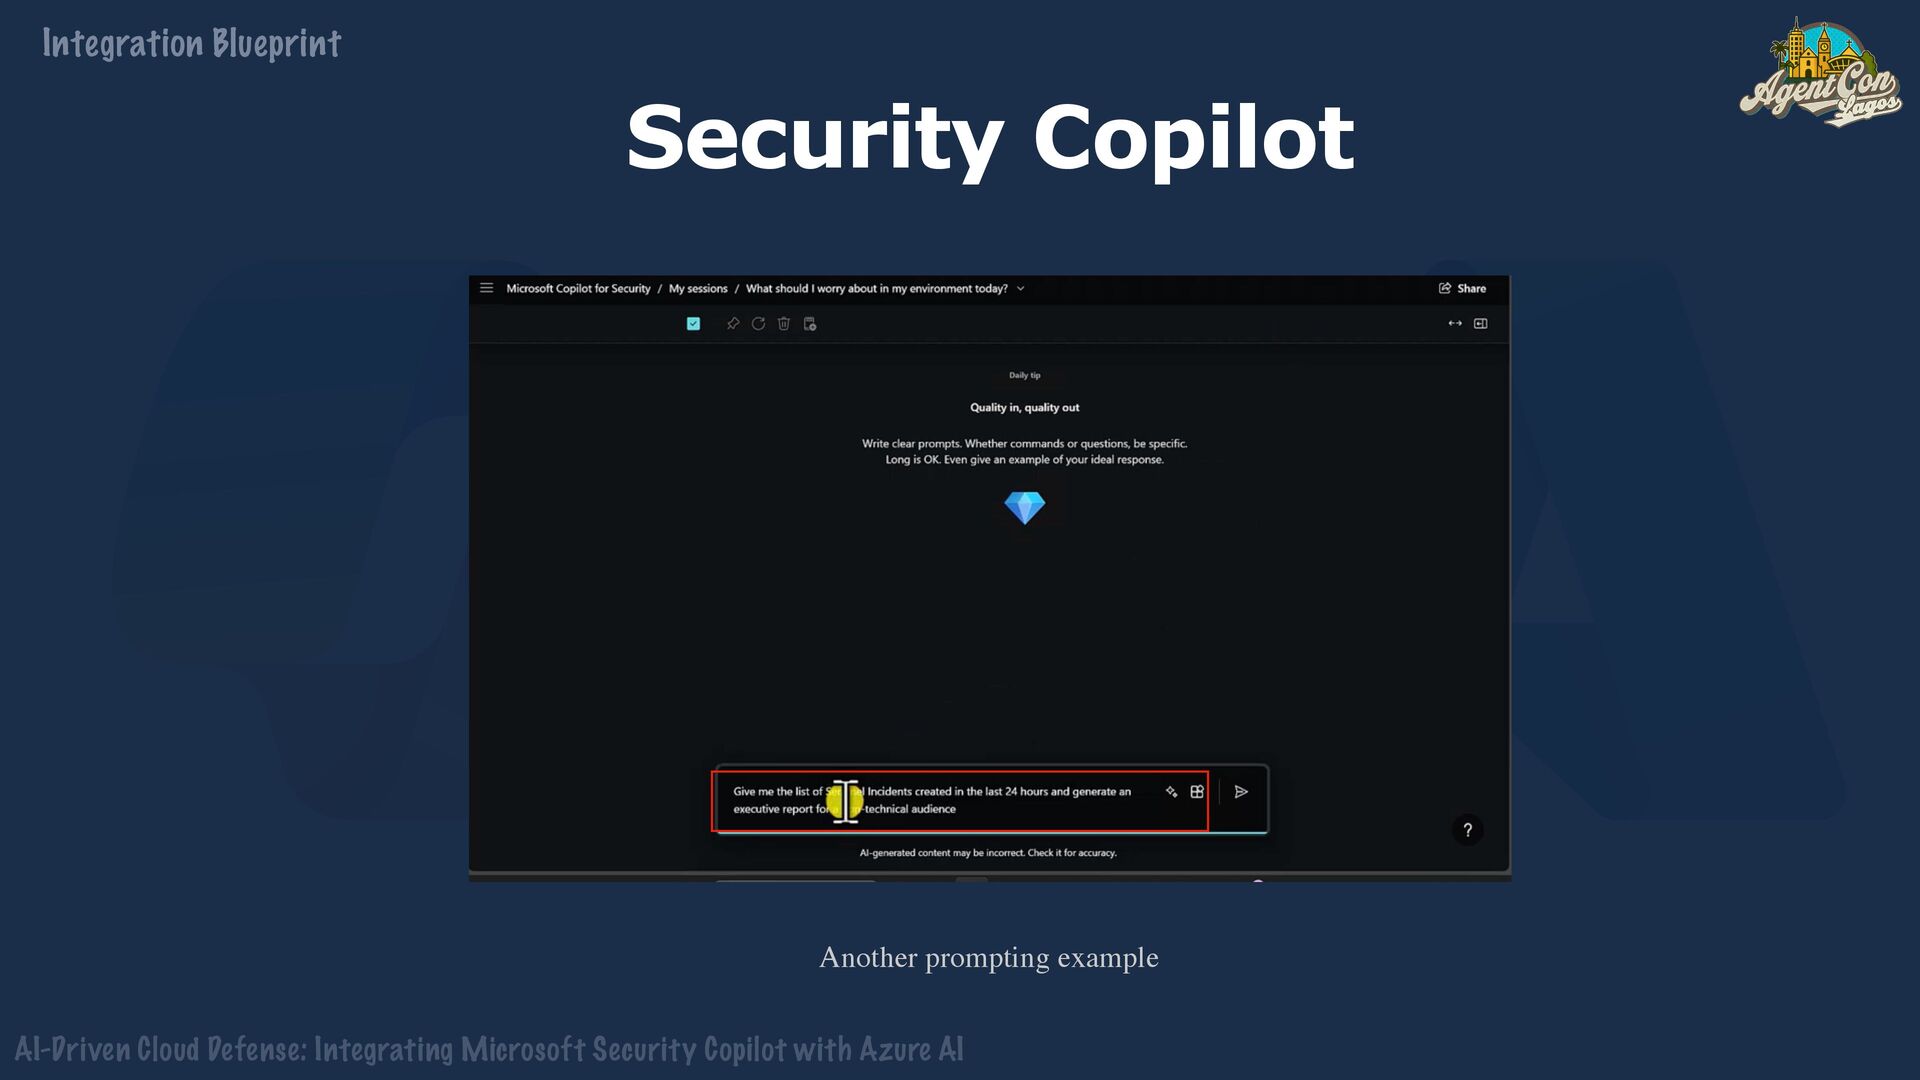
    AI Security Copilot Integration Blueprint Another prompting example
  24. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

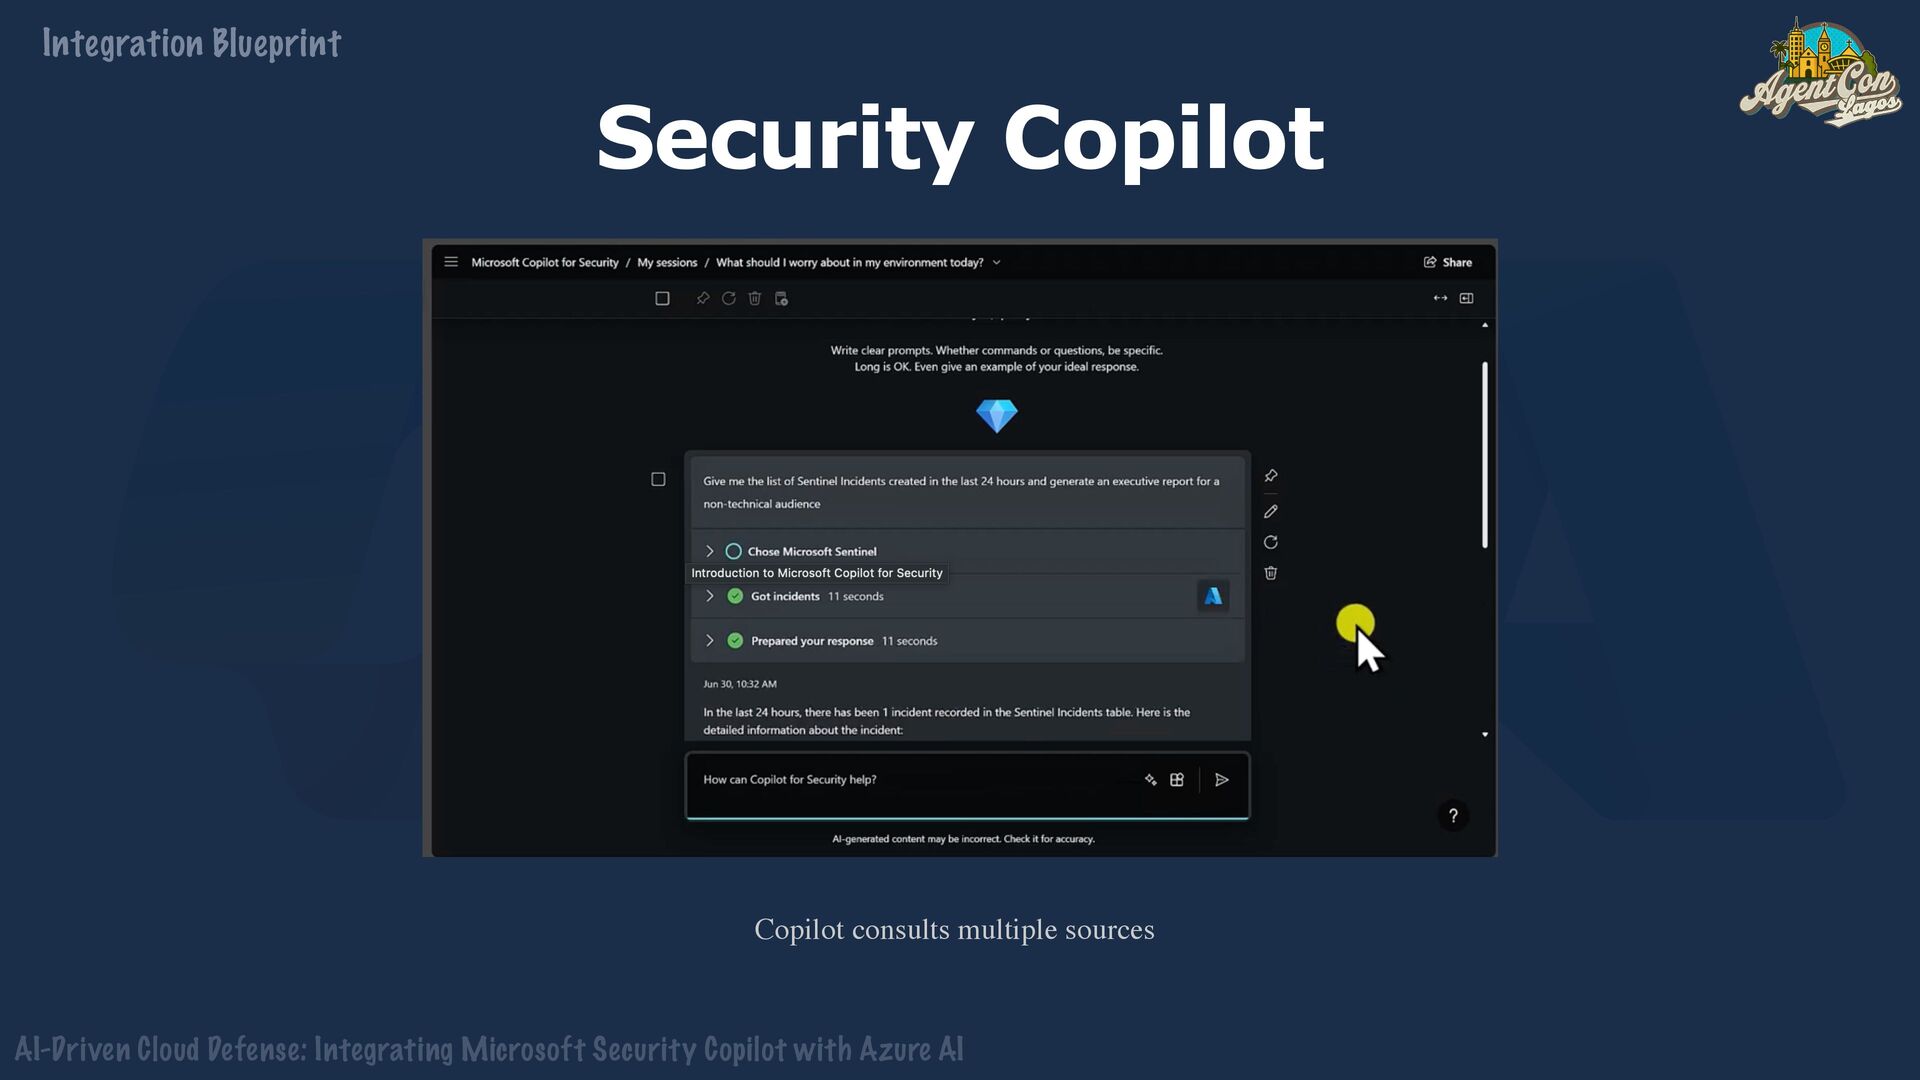
    AI Security Copilot Integration Blueprint Copilot consults multiple sources
  25. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

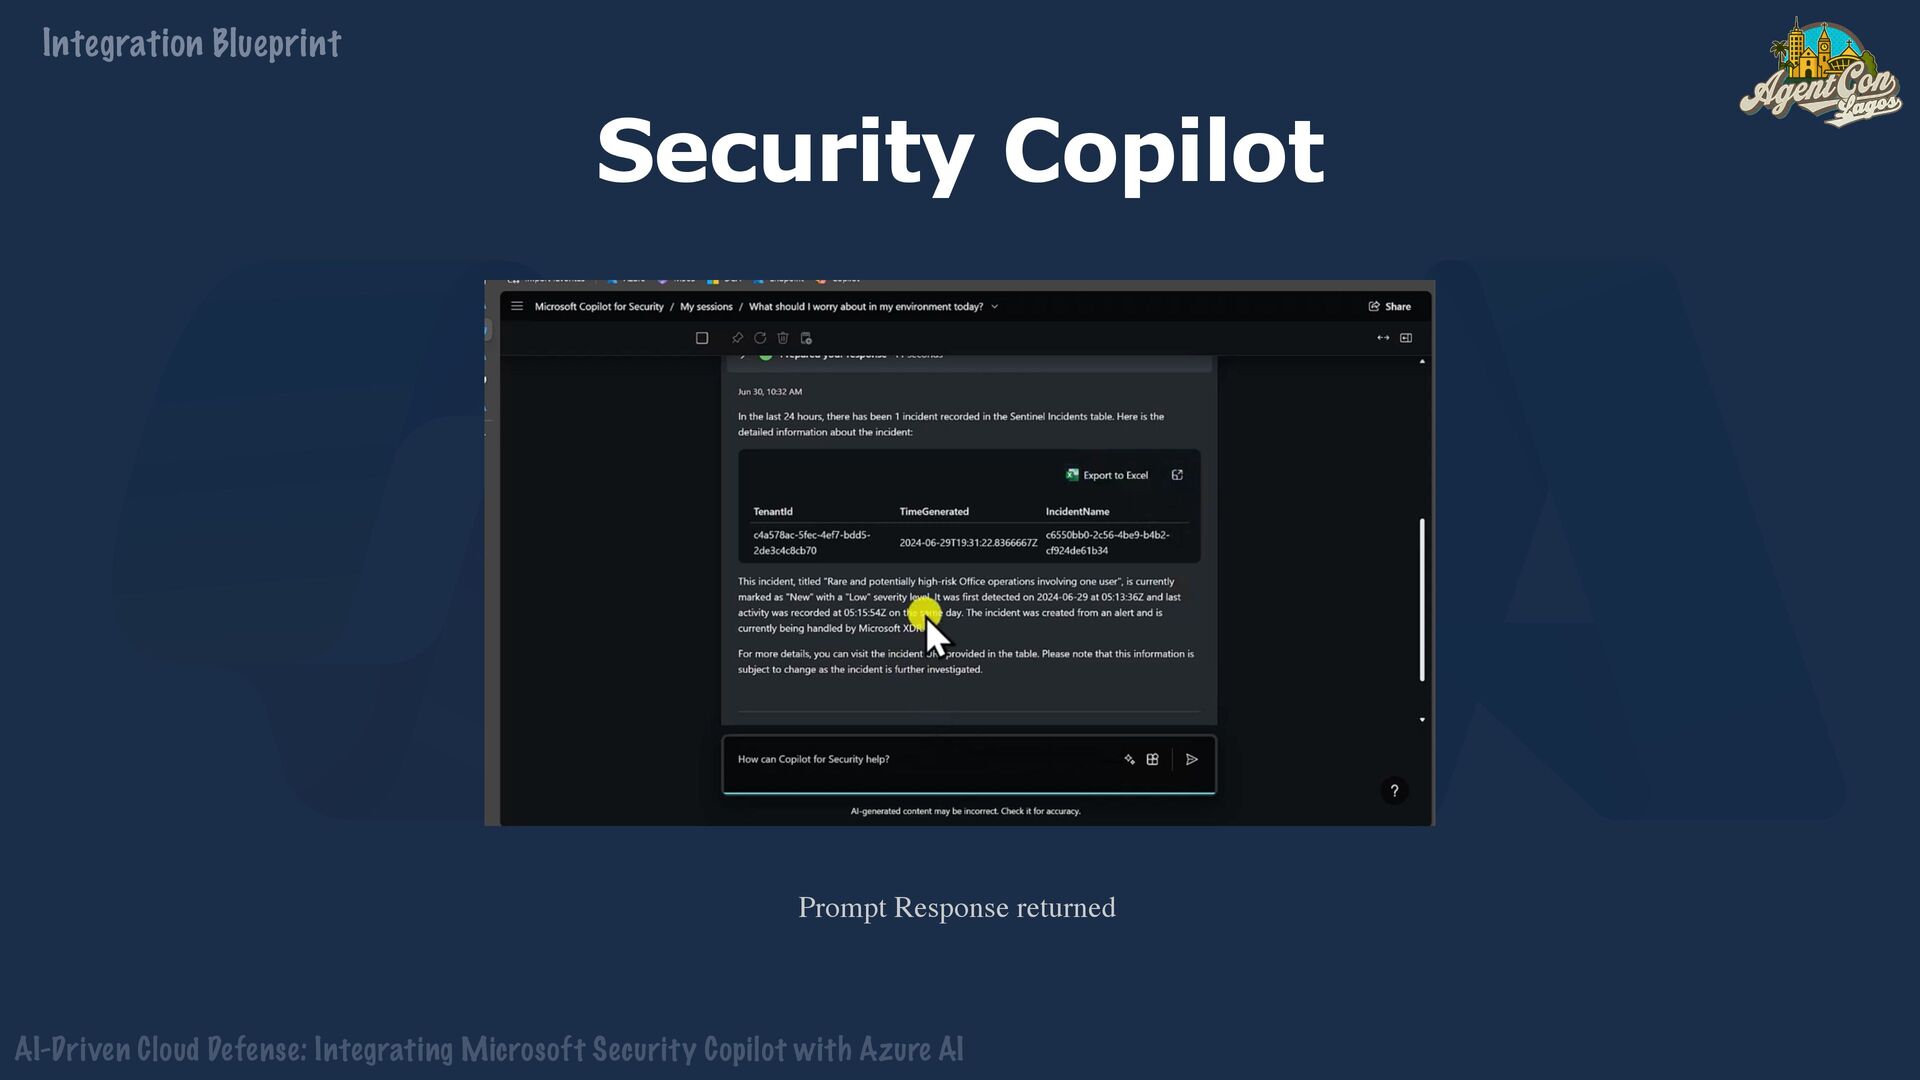
    AI Security Copilot Integration Blueprint Prompt Response returned
  26. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

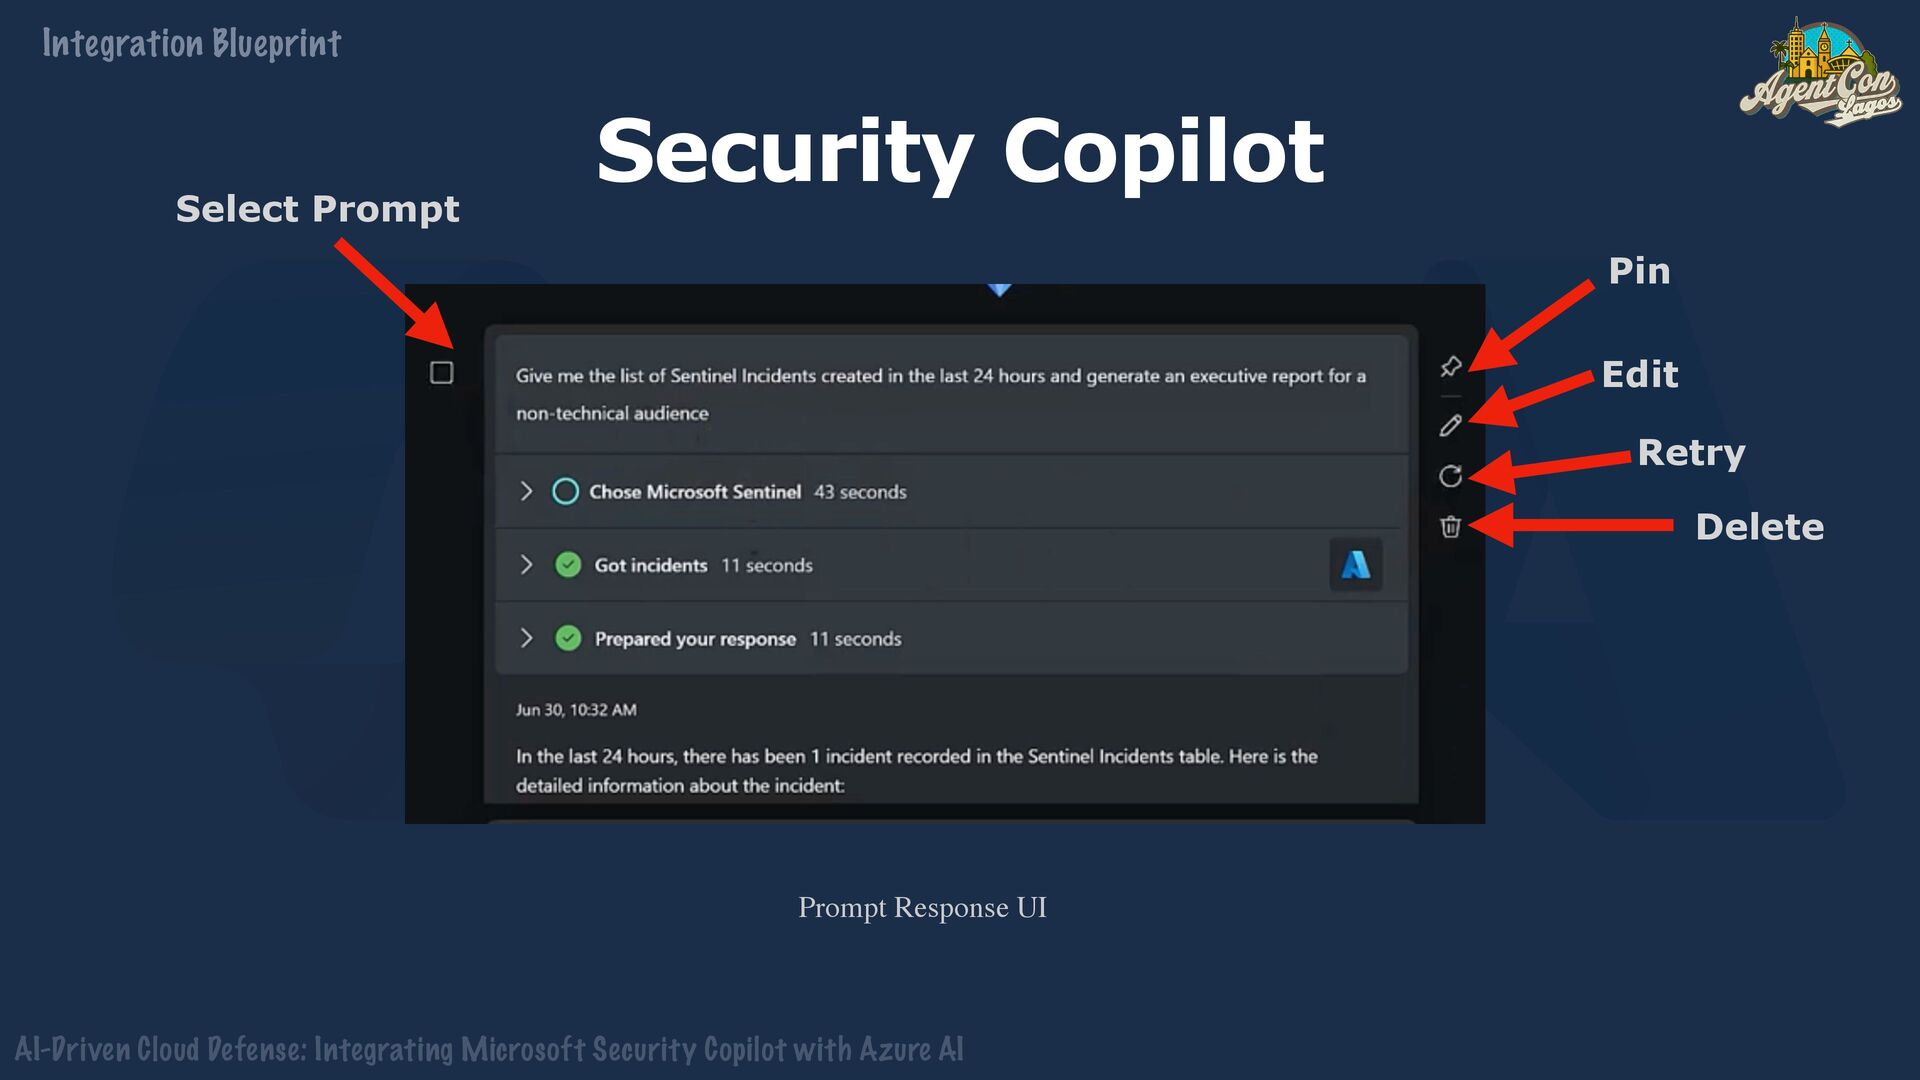
    AI Select Prompt Pin Edit Retry Delete Security Copilot Integration Blueprint Prompt Response UI
  27. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

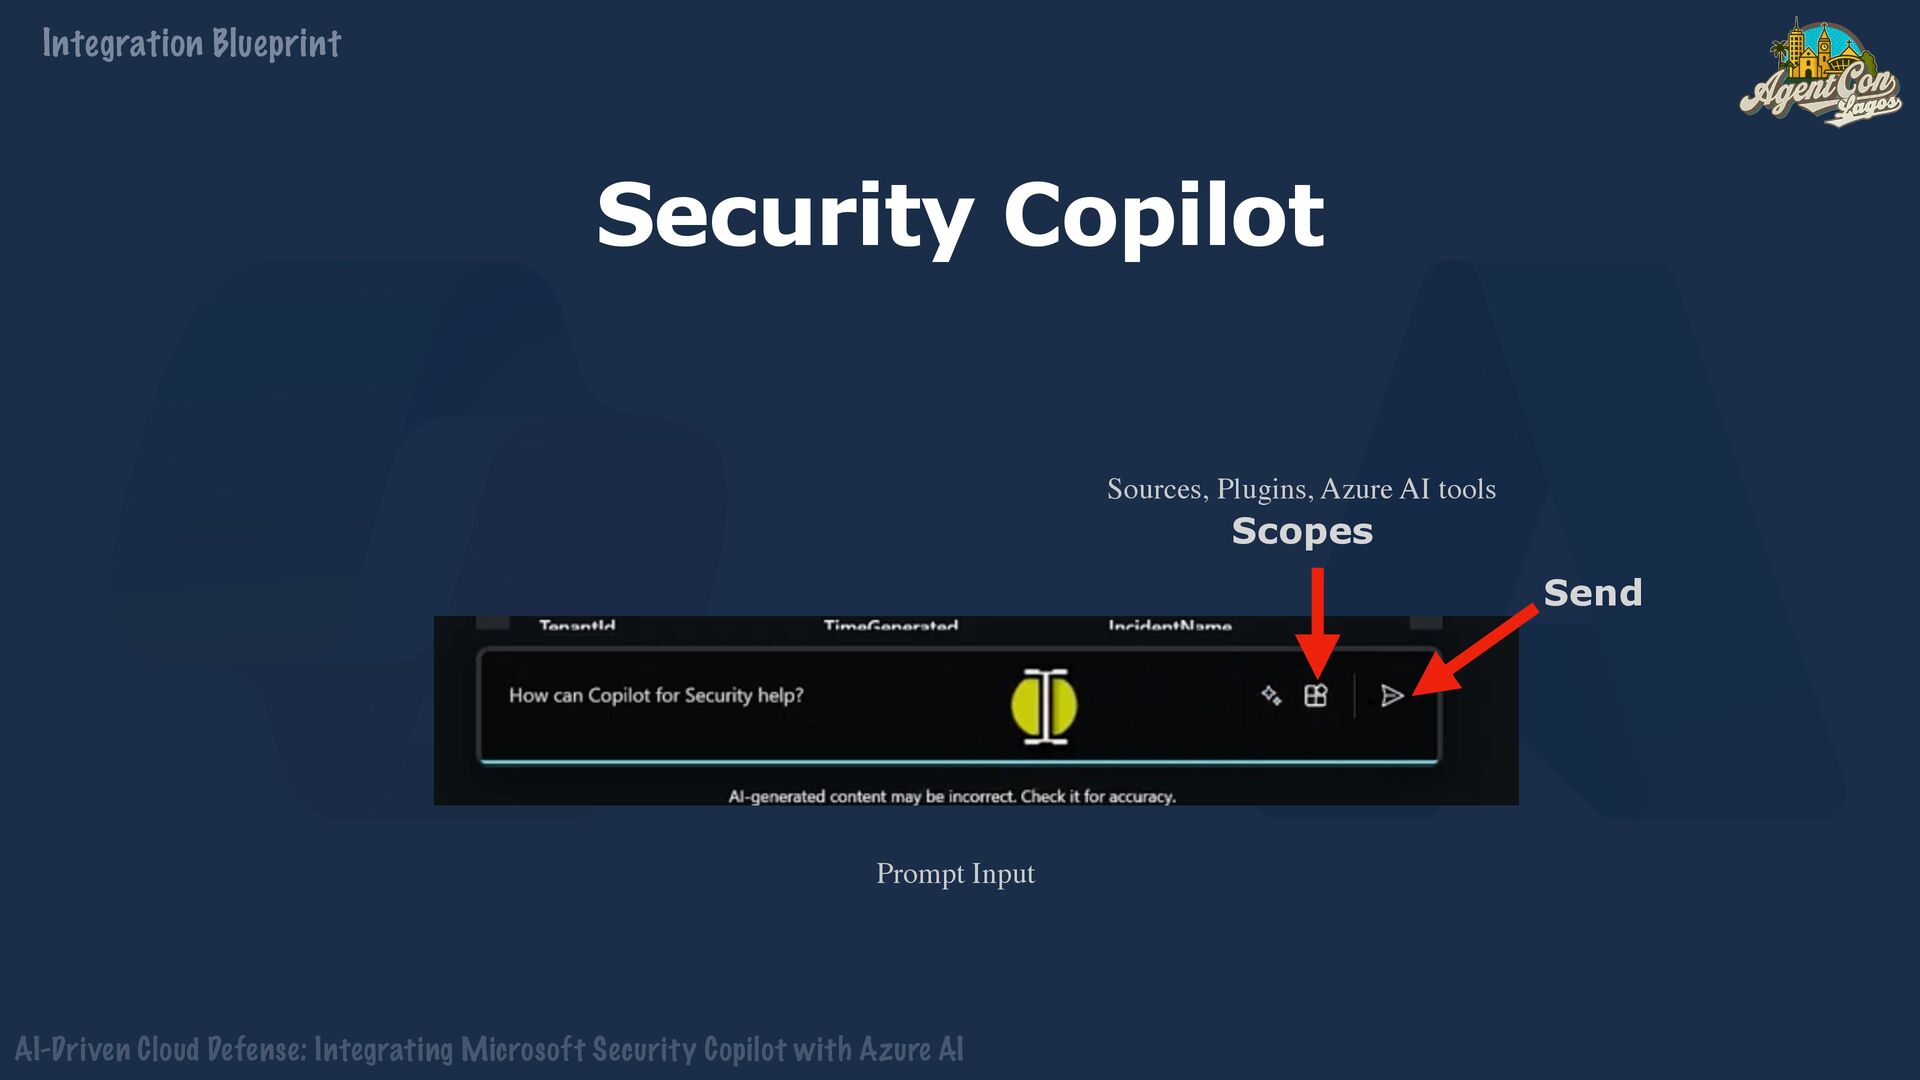
    AI Scopes Send Security Copilot Integration Blueprint Prompt Input Sources, Plugins, Azure AI tools
  28. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

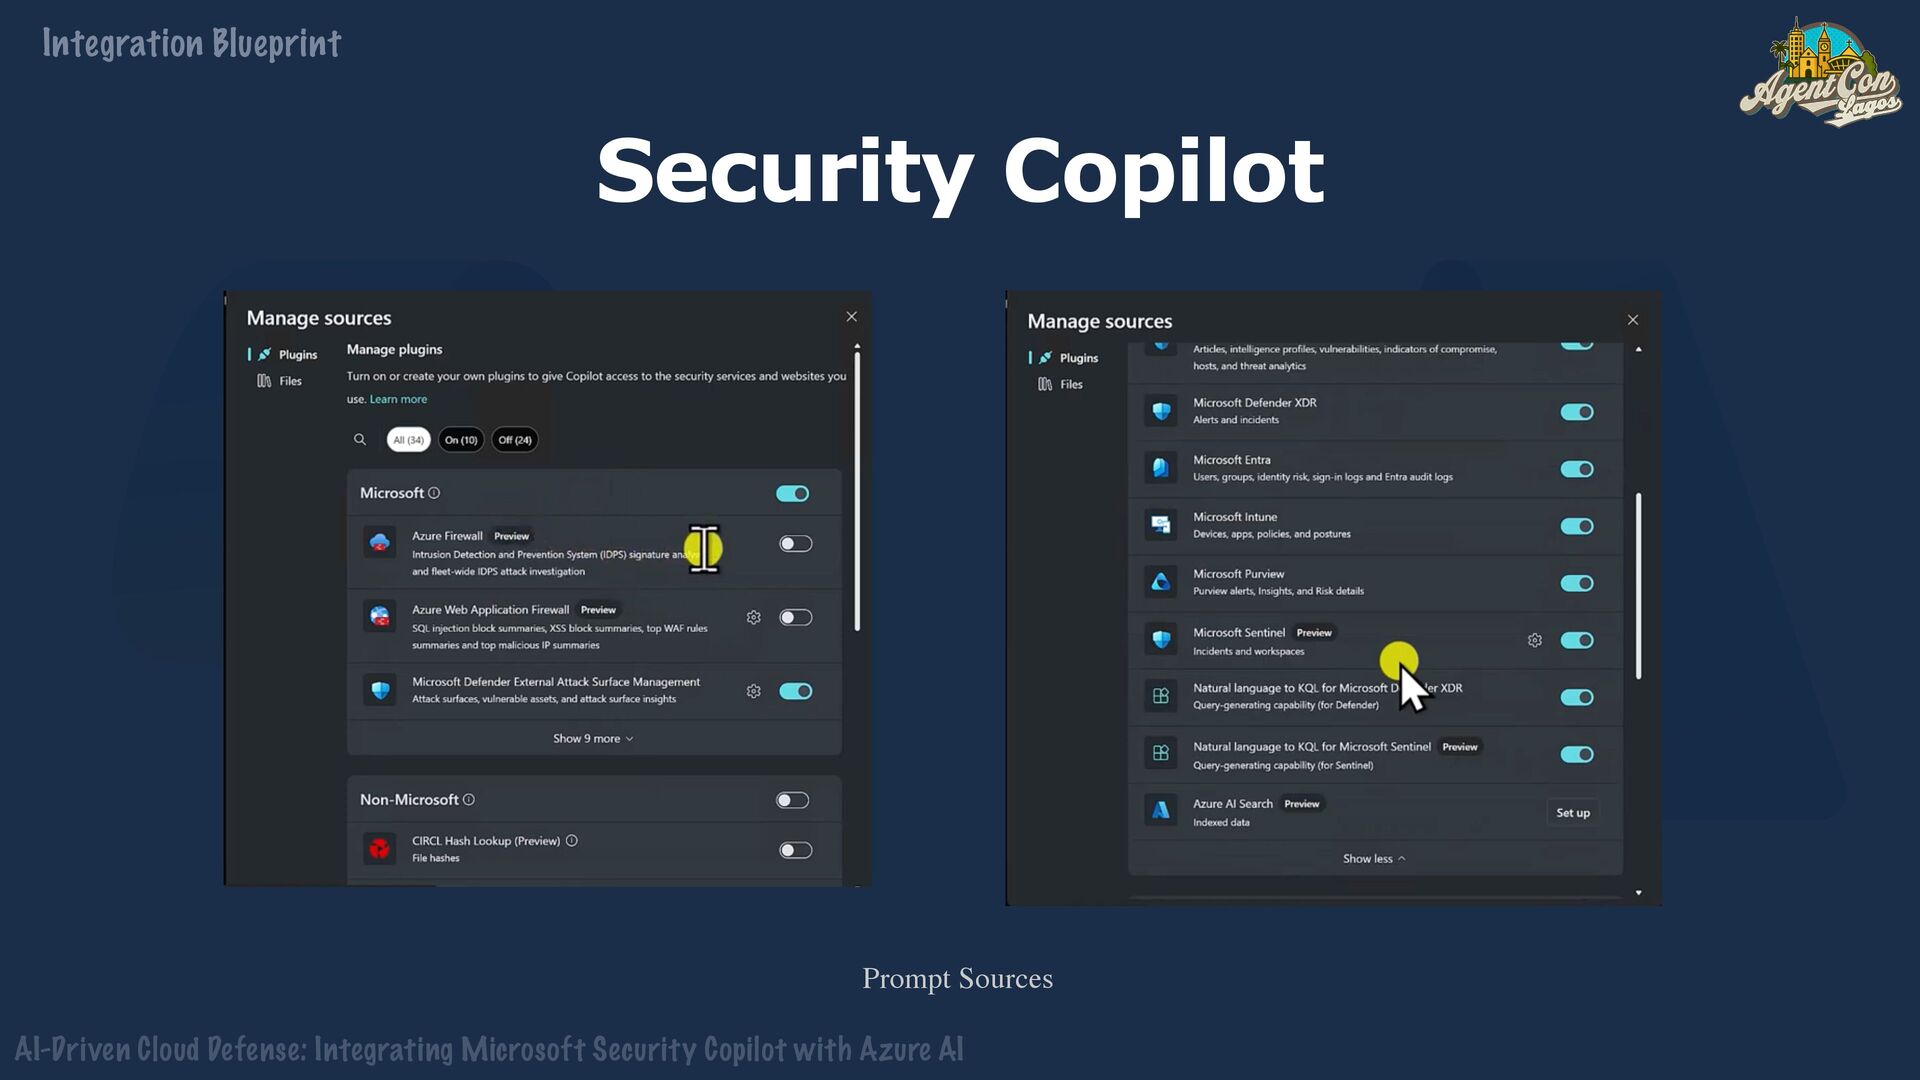
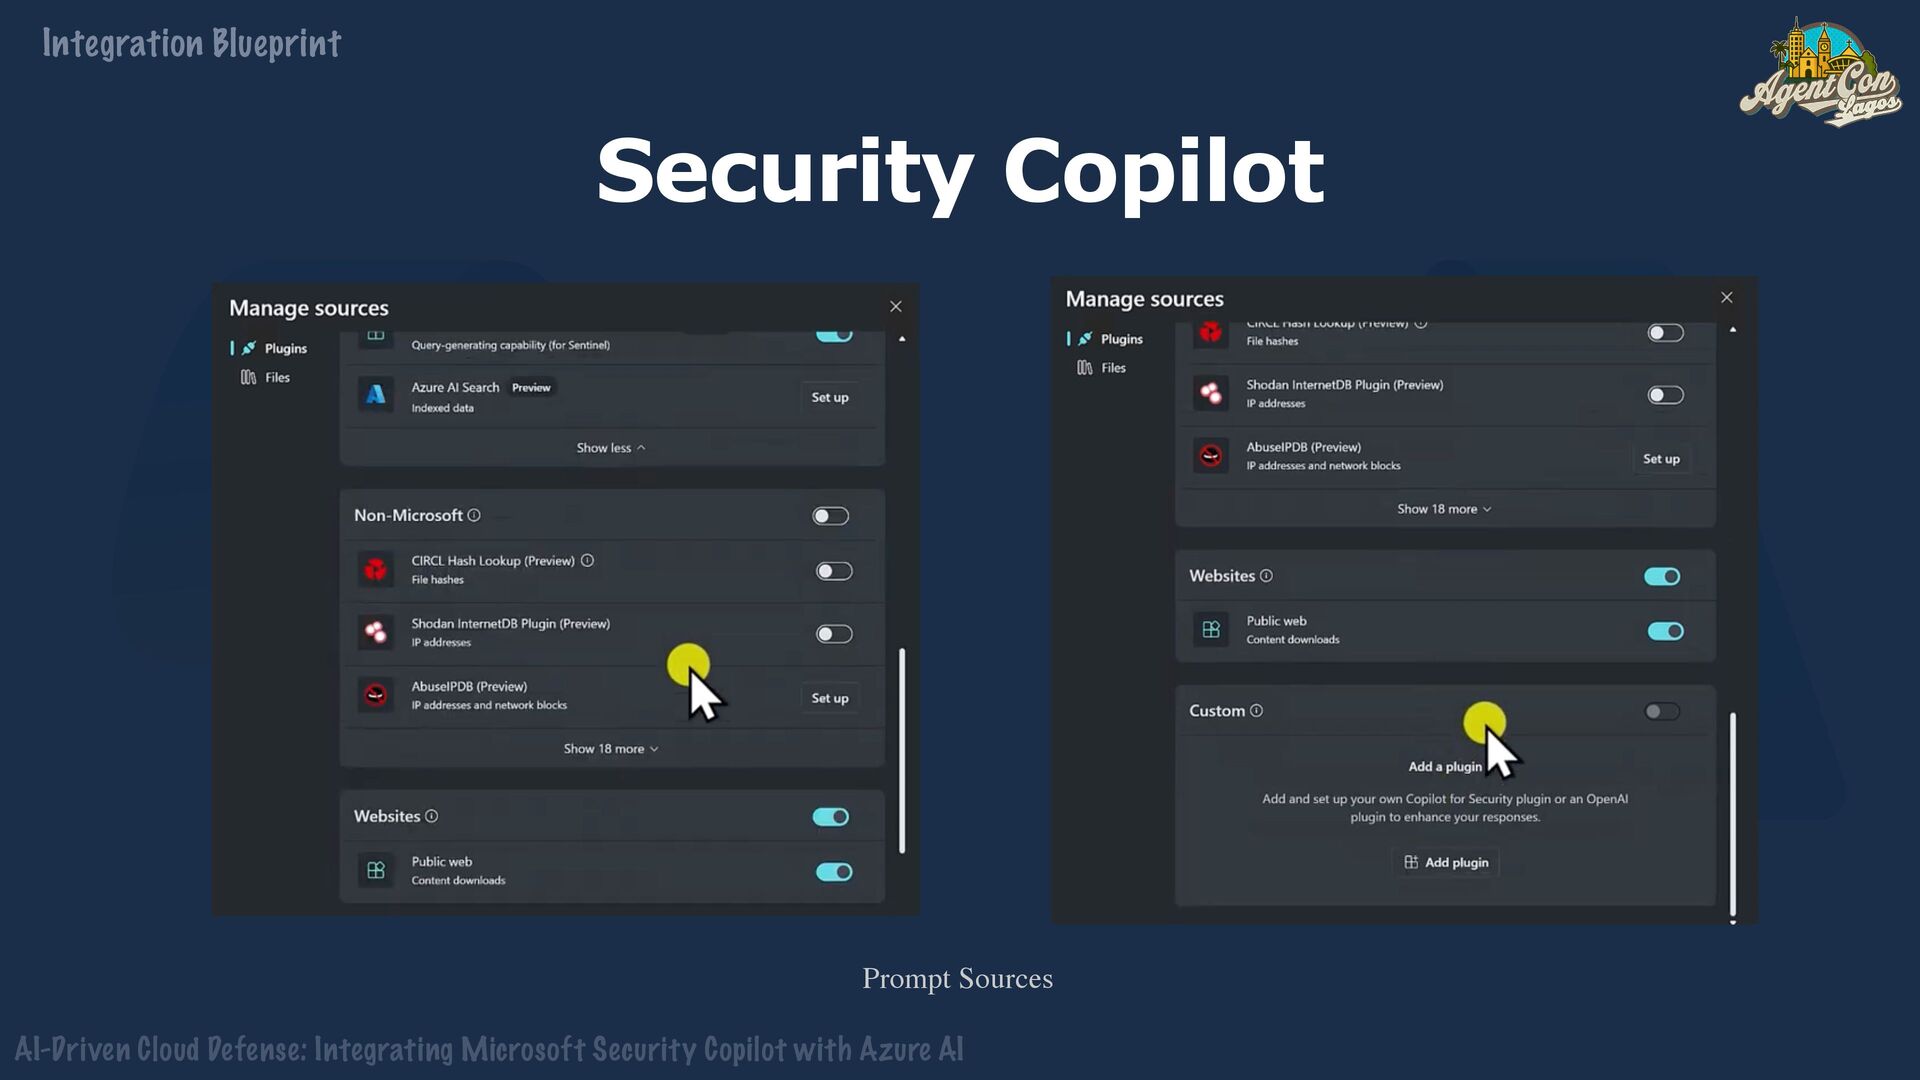
    AI Security Copilot Integration Blueprint Prompt Sources
  29. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Prompt Sources Security Copilot Integration Blueprint
  30. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

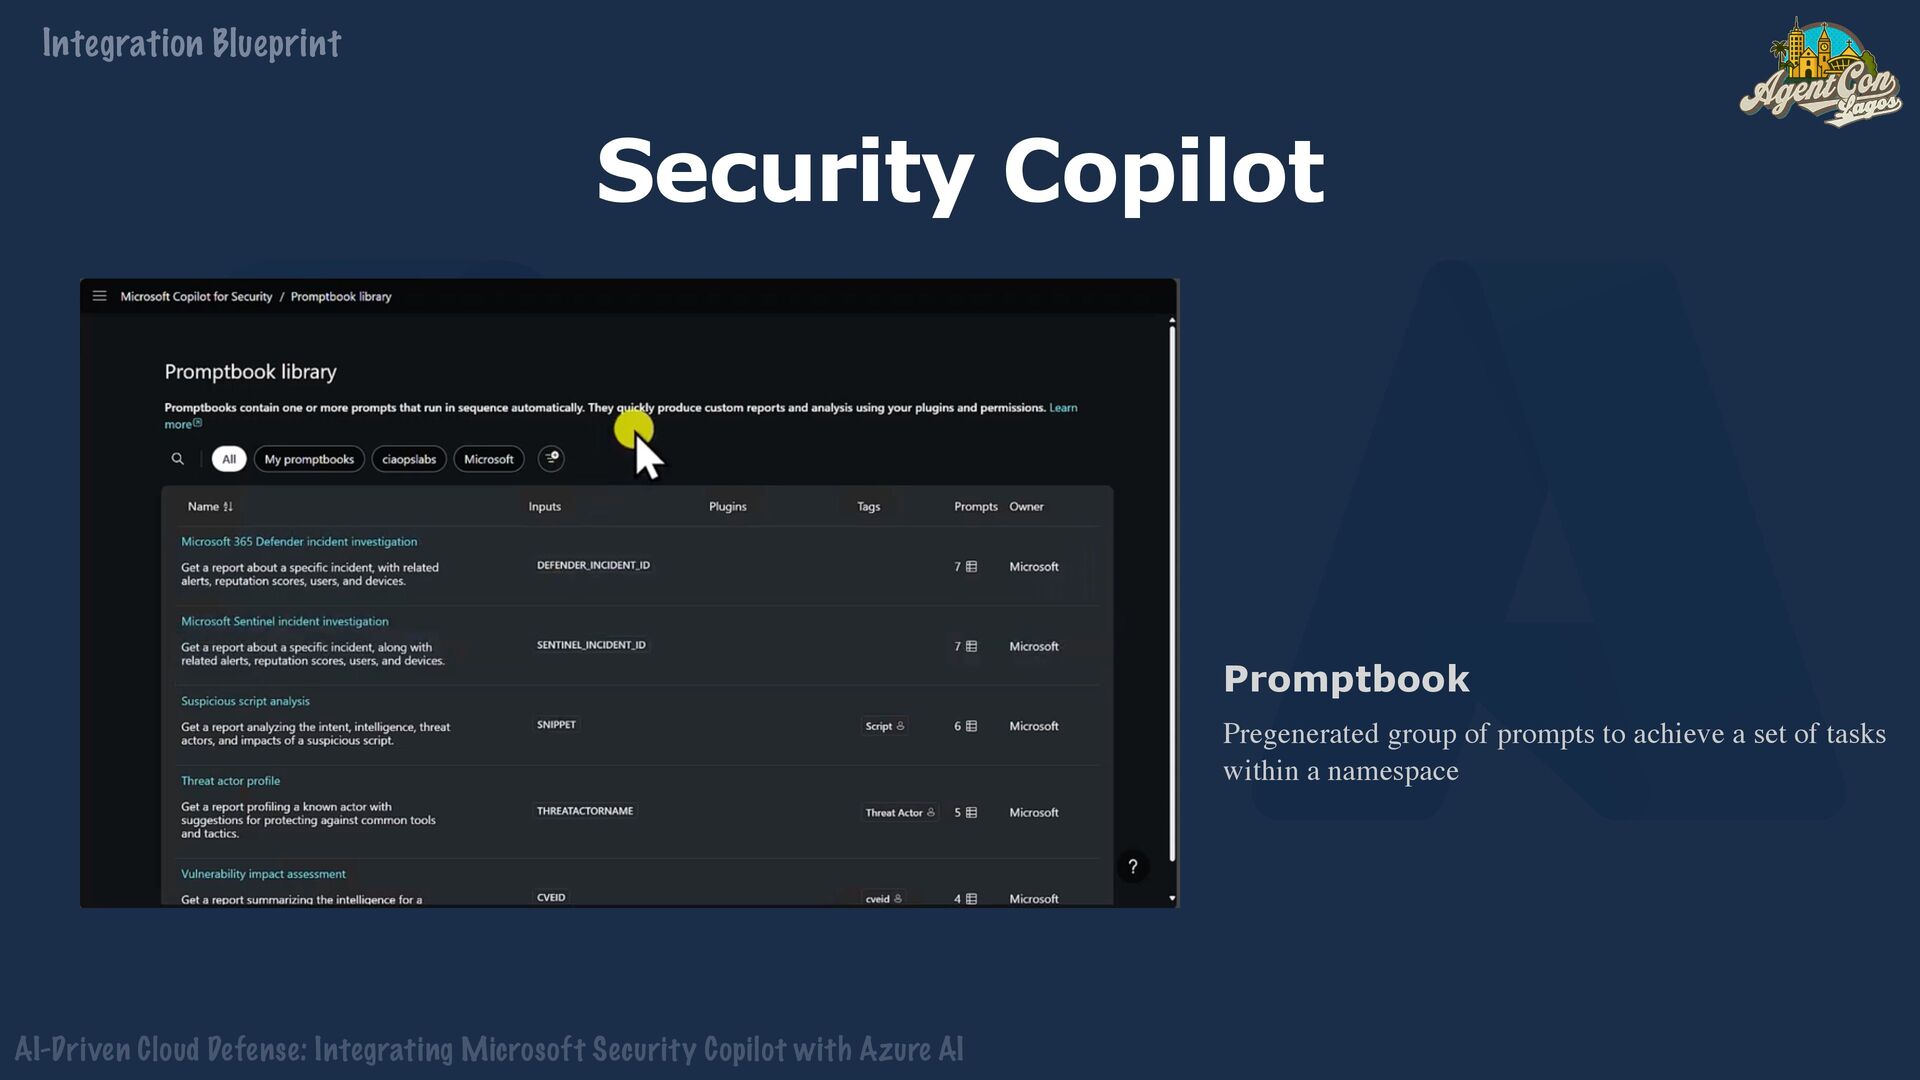
    AI Pregenerated group of prompts to achieve a set of tasks within a namespace Promptbook Security Copilot Integration Blueprint
  31. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

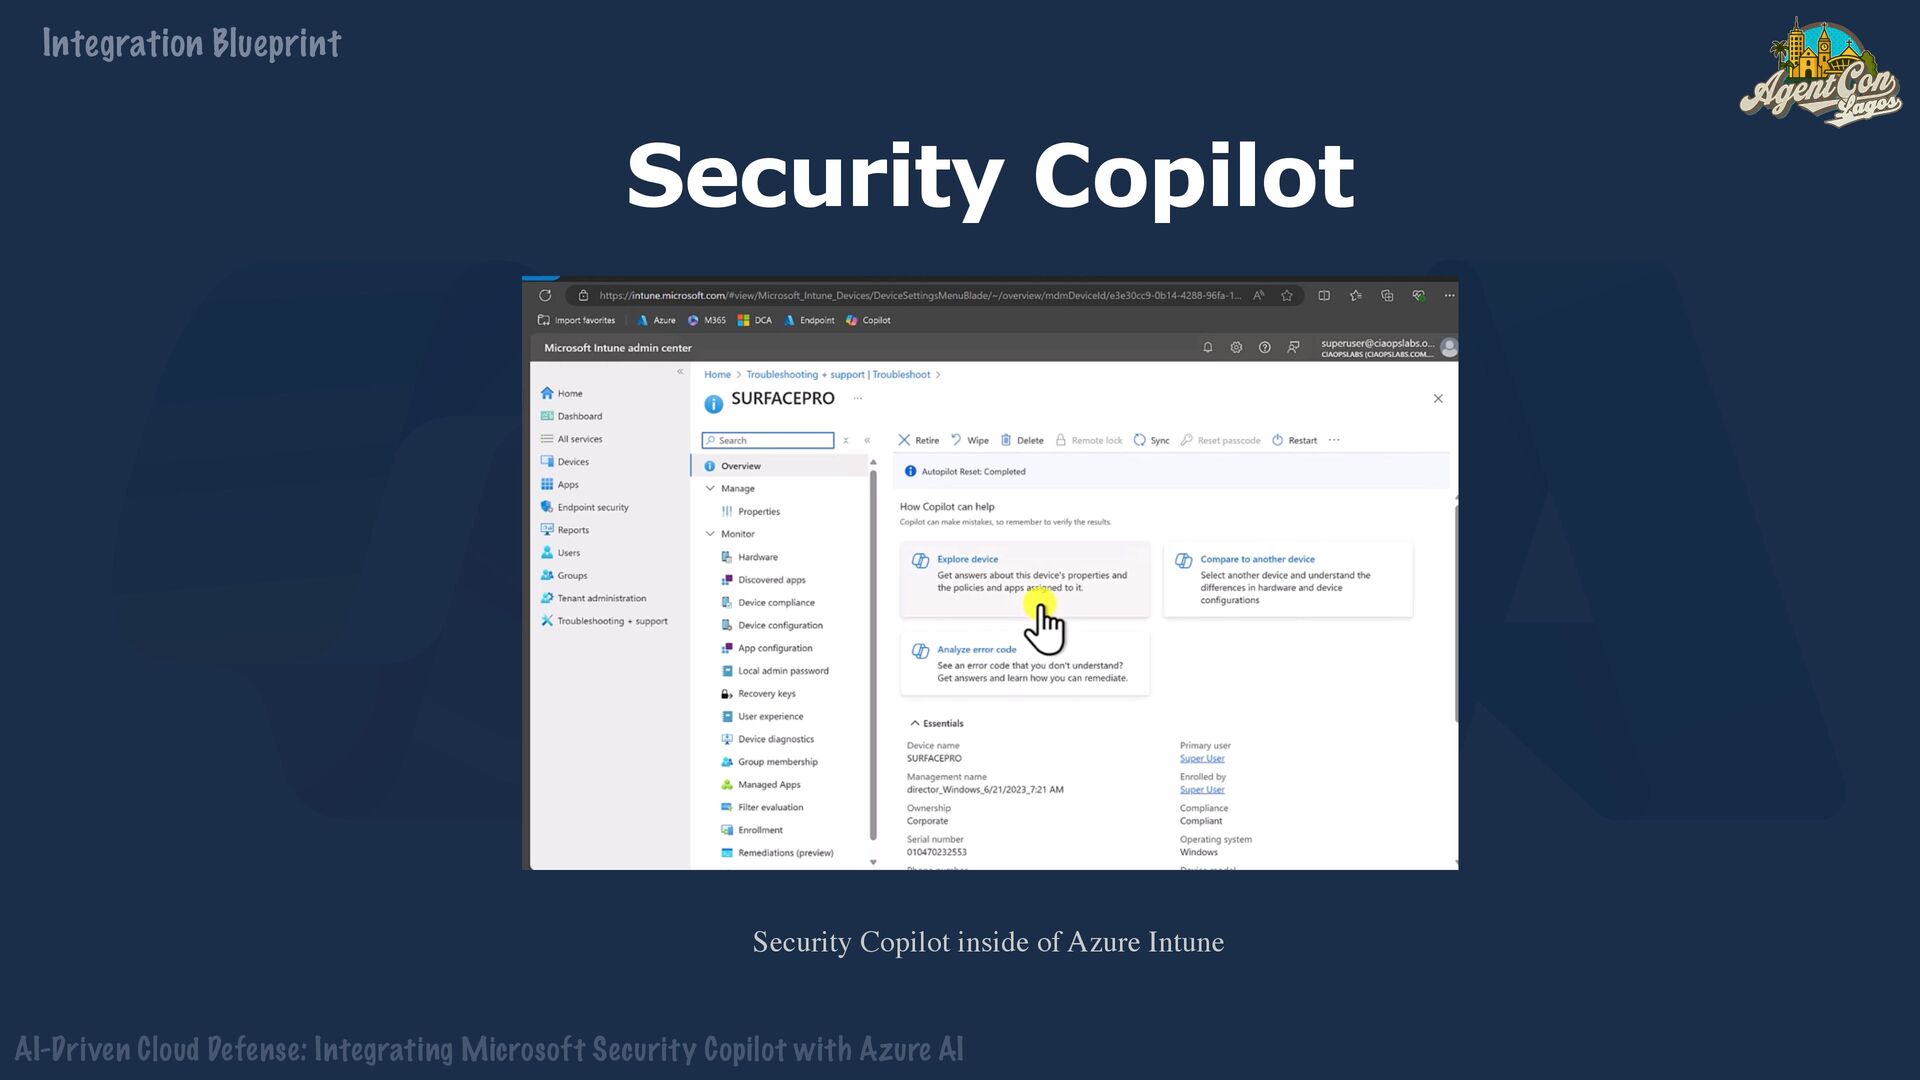
    AI Security Copilot Integration Blueprint Security Copilot inside of Azure Intune
  32. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

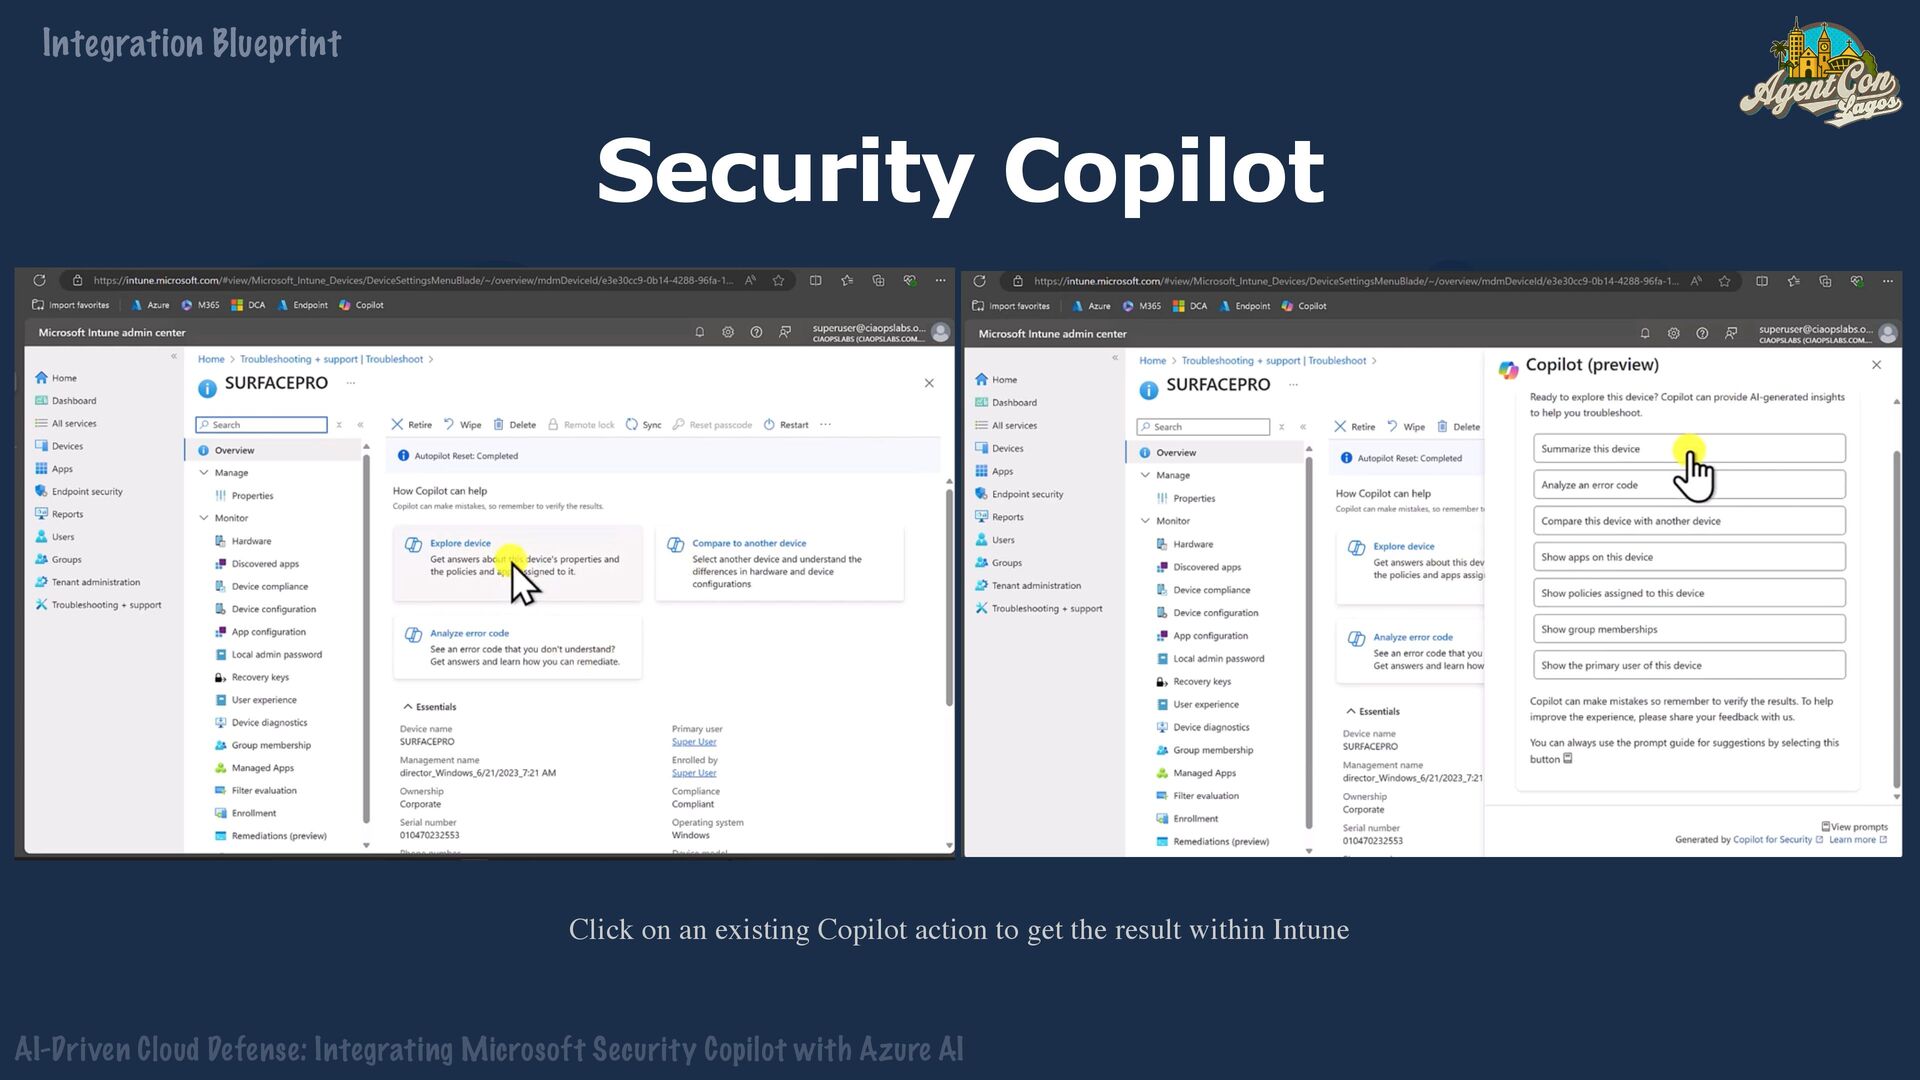
    AI Security Copilot Integration Blueprint Click on an existing Copilot action to get the result within Intune
  33. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

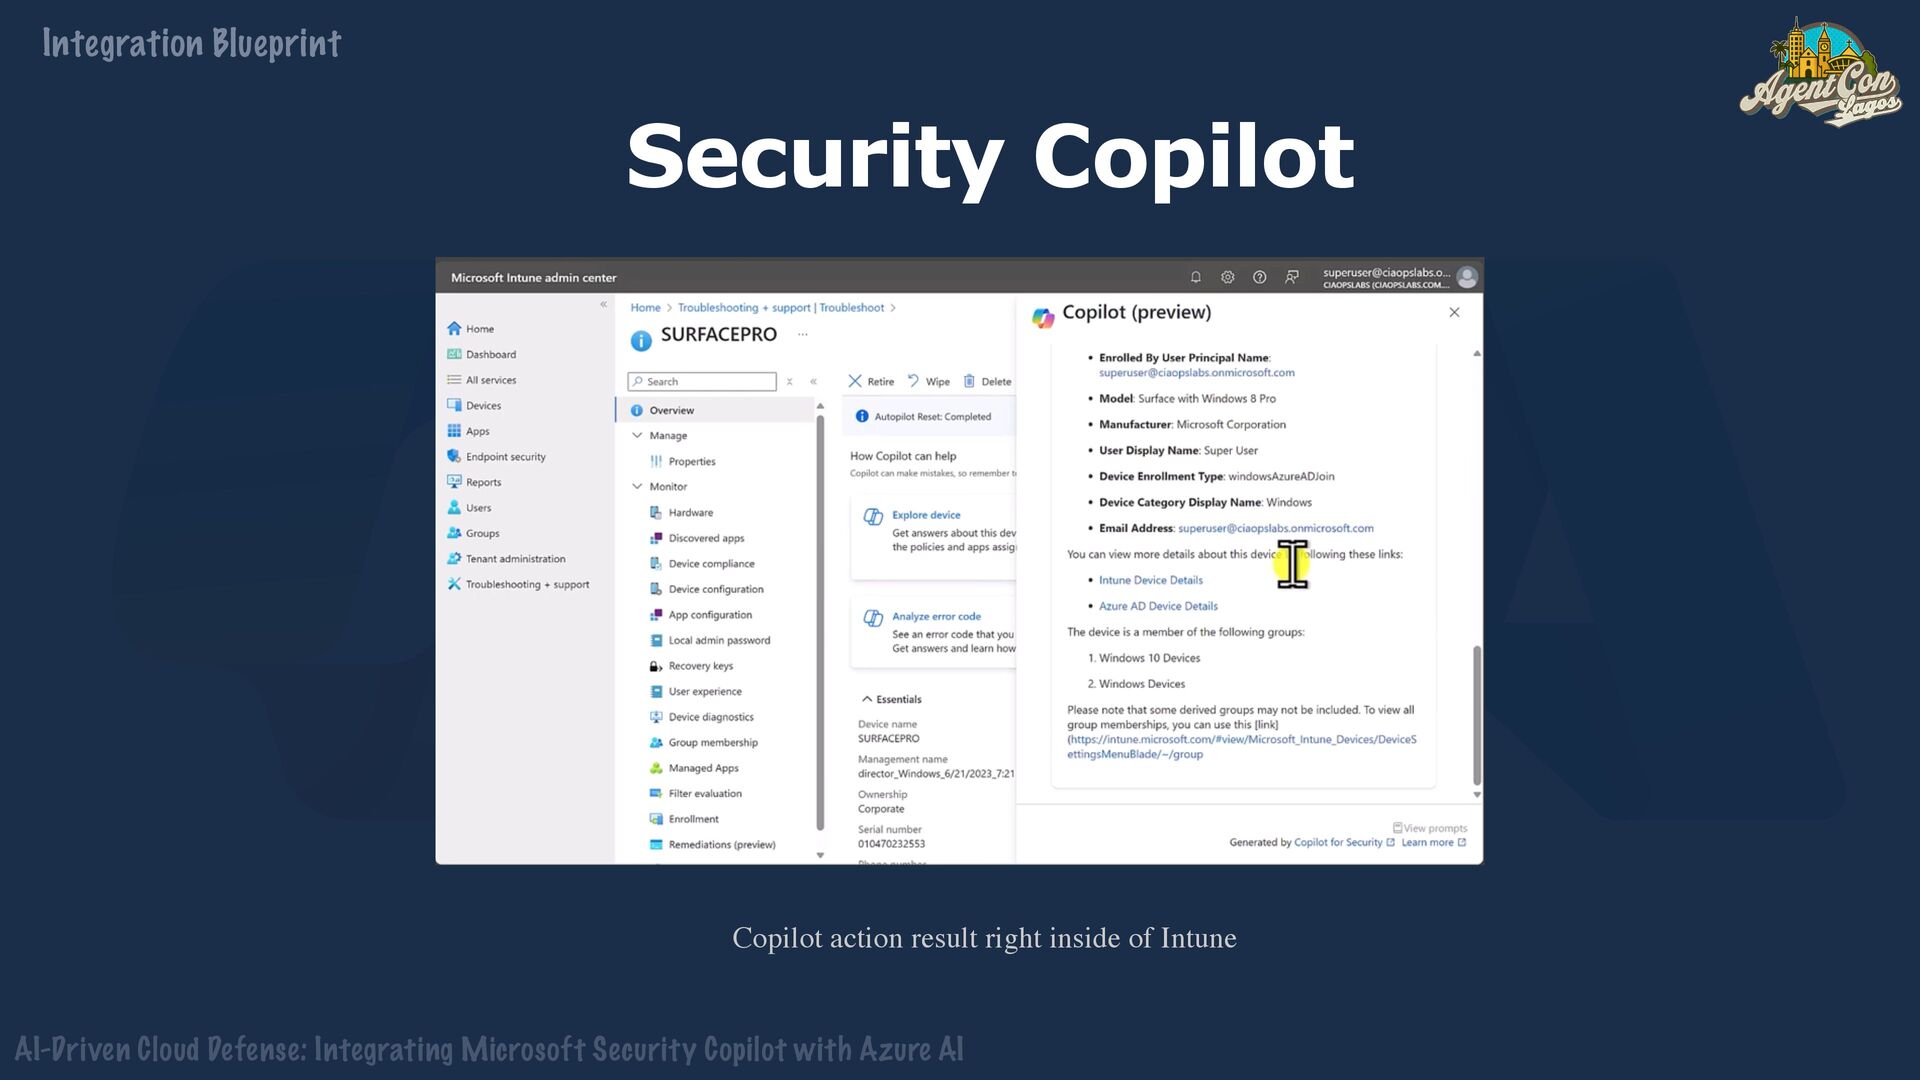
    AI Copilot action result right inside of Intune Security Copilot Integration Blueprint
  34. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

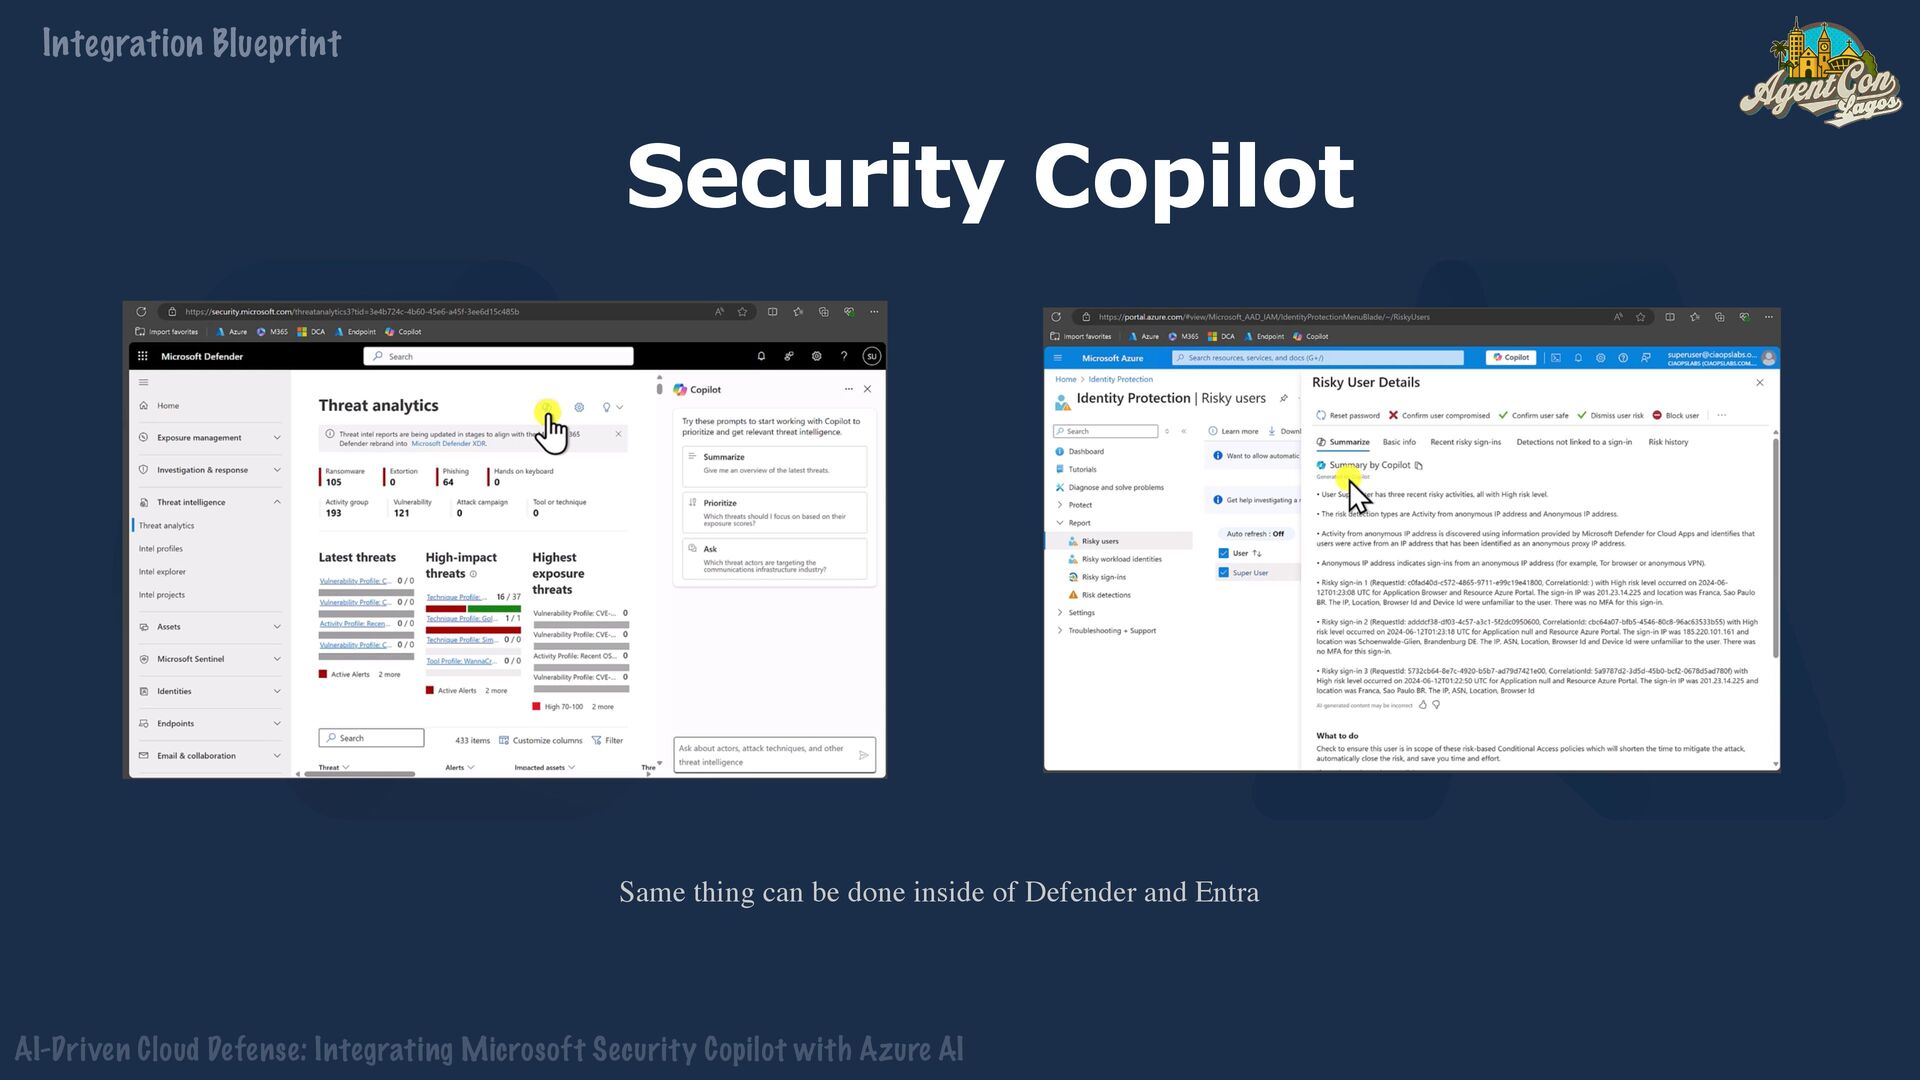
    AI Same thing can be done inside of Defender and Entra Security Copilot Integration Blueprint
  35. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Automating Workflows Automated Responses Faster resolution times through automated responses Enhanced Operational Efficiency Automating routine tasks allows focus on complex issues Faster Incident Responses Reduced response times, improving overall security posture
  36. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Sentinel Playbooks A series of steps that can be taken after one another, which can be applied when there is a specific condition. For example, a specific alert, incident is triggered within a specific sentinel environment They provide workflow automation via logic apps, and help SOC team automate decision-making
  37. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

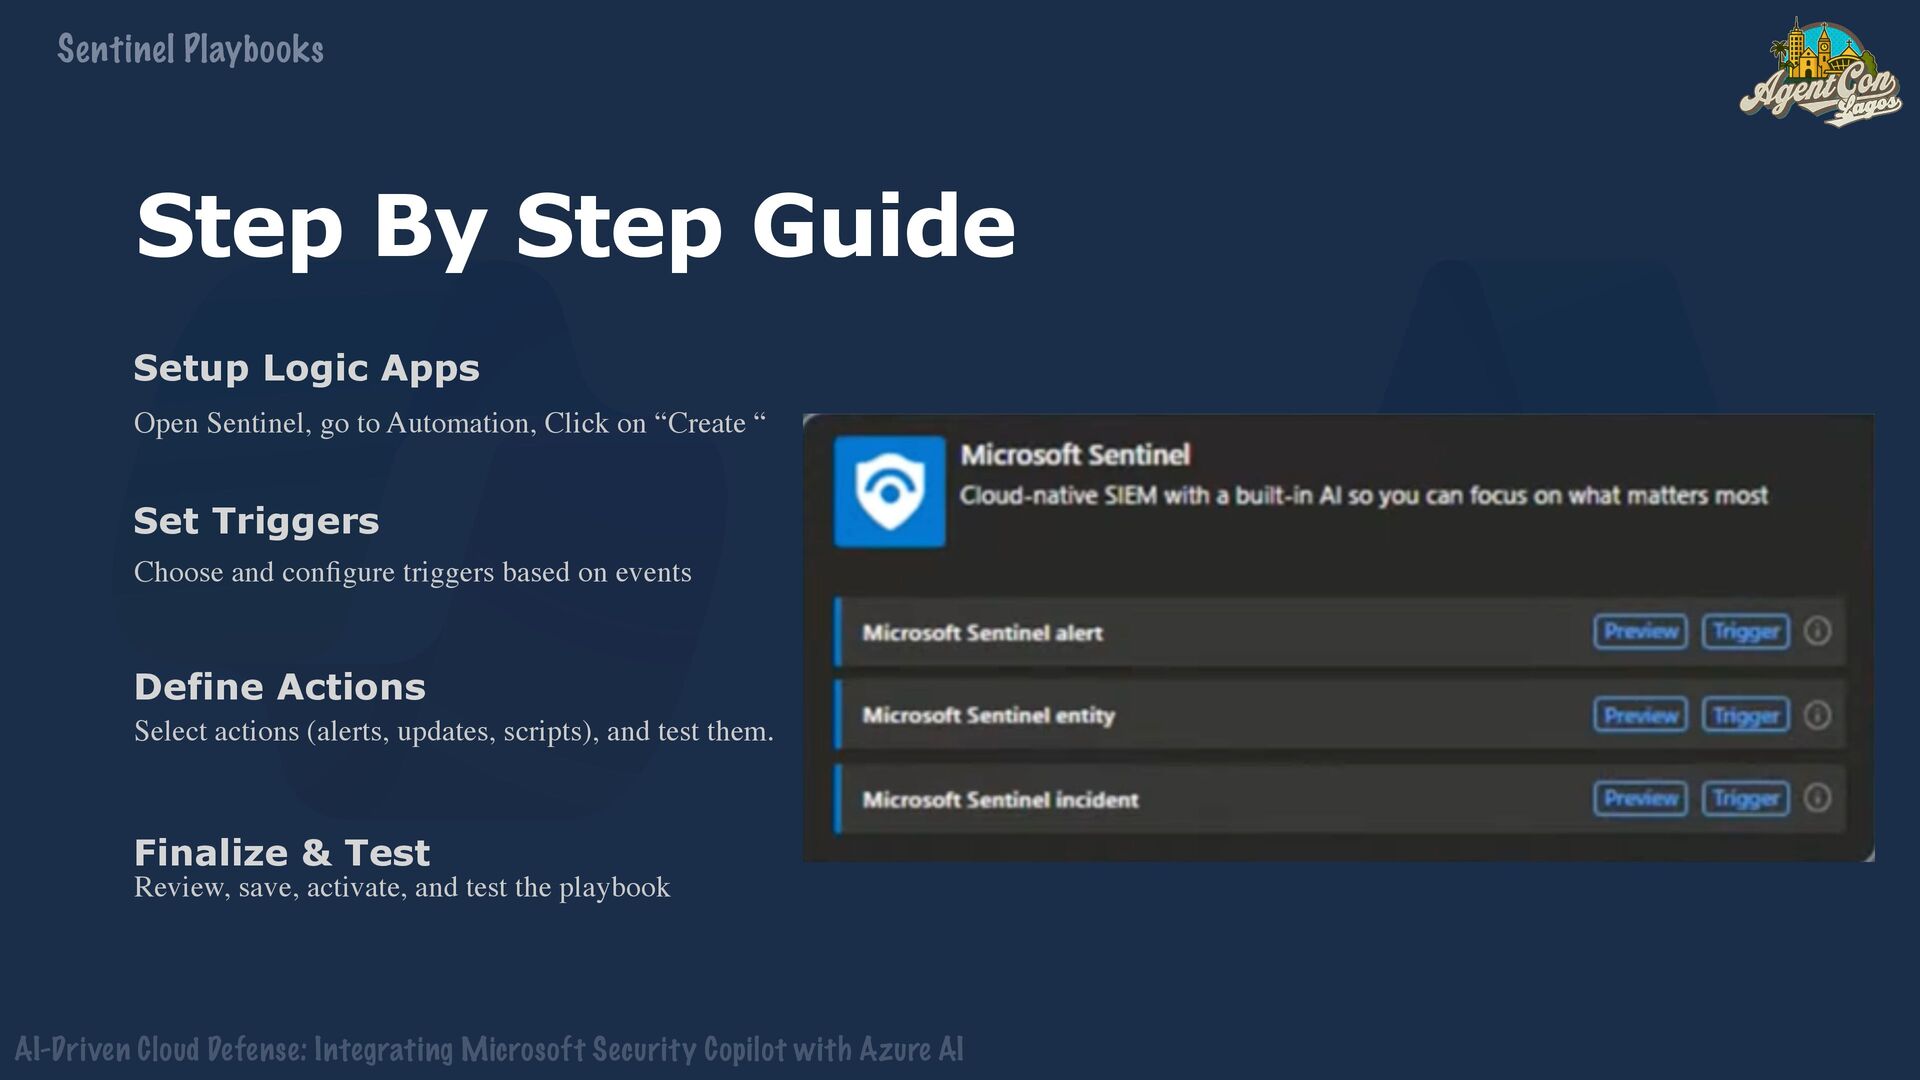
    AI Step By Step Guide Sentinel Playbooks Setup Logic Apps Open Sentinel, go to Automation, Click on “Create “ Set Triggers Choose and con fi gure triggers based on events Define Actions Select actions (alerts, updates, scripts), and test them. Finalize & Test Review, save, activate, and test the playbook
  38. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

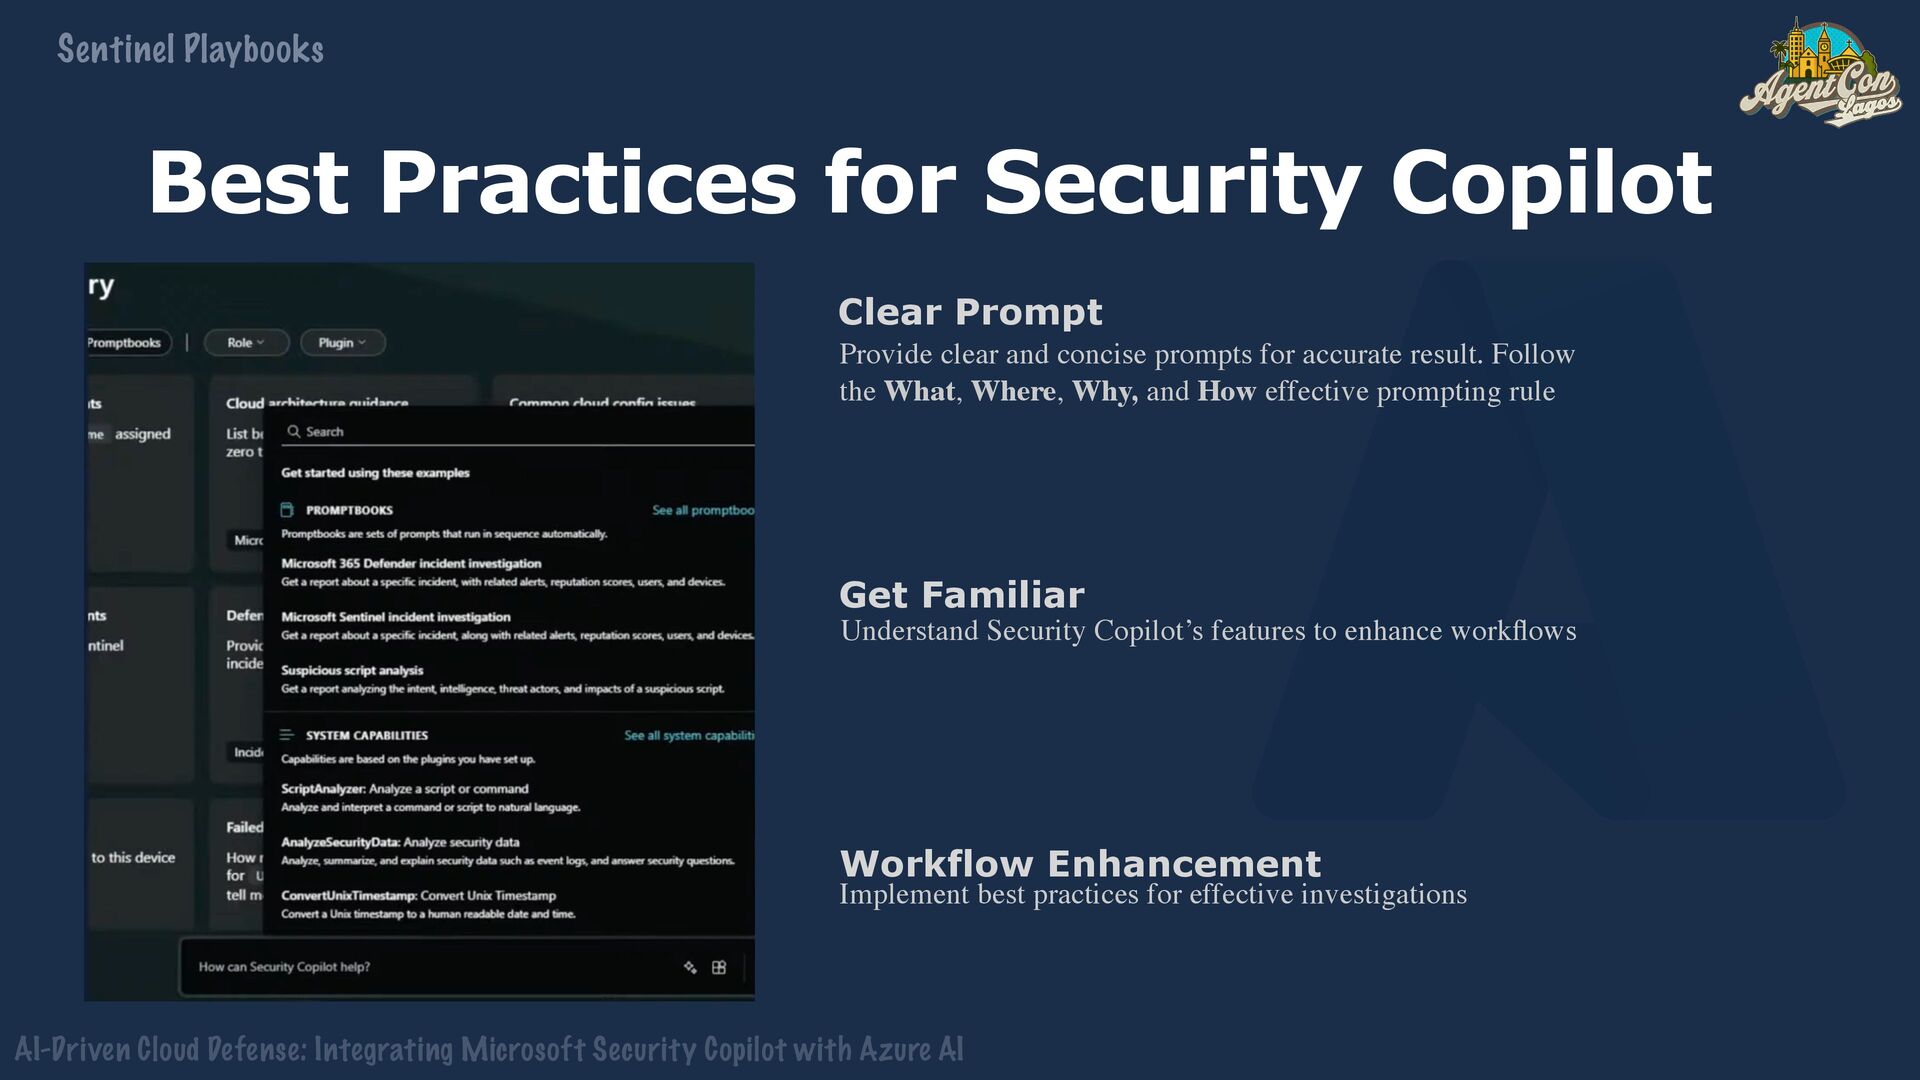
    AI Sentinel Playbooks Best Practices for Security Copilot Clear Prompt Provide clear and concise prompts for accurate result. Follow the What, Where, Why, and How effective prompting rule Get Familiar Understand Security Copilot’s features to enhance work fl ows Workflow Enhancement Implement best practices for effective investigations
  39. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Sentinel Playbooks Why Automate Context Aware Bring different context as they are available Remove Limitation They can run 24/7 Scale Run on Azure Cloud Infrastructure
  40. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

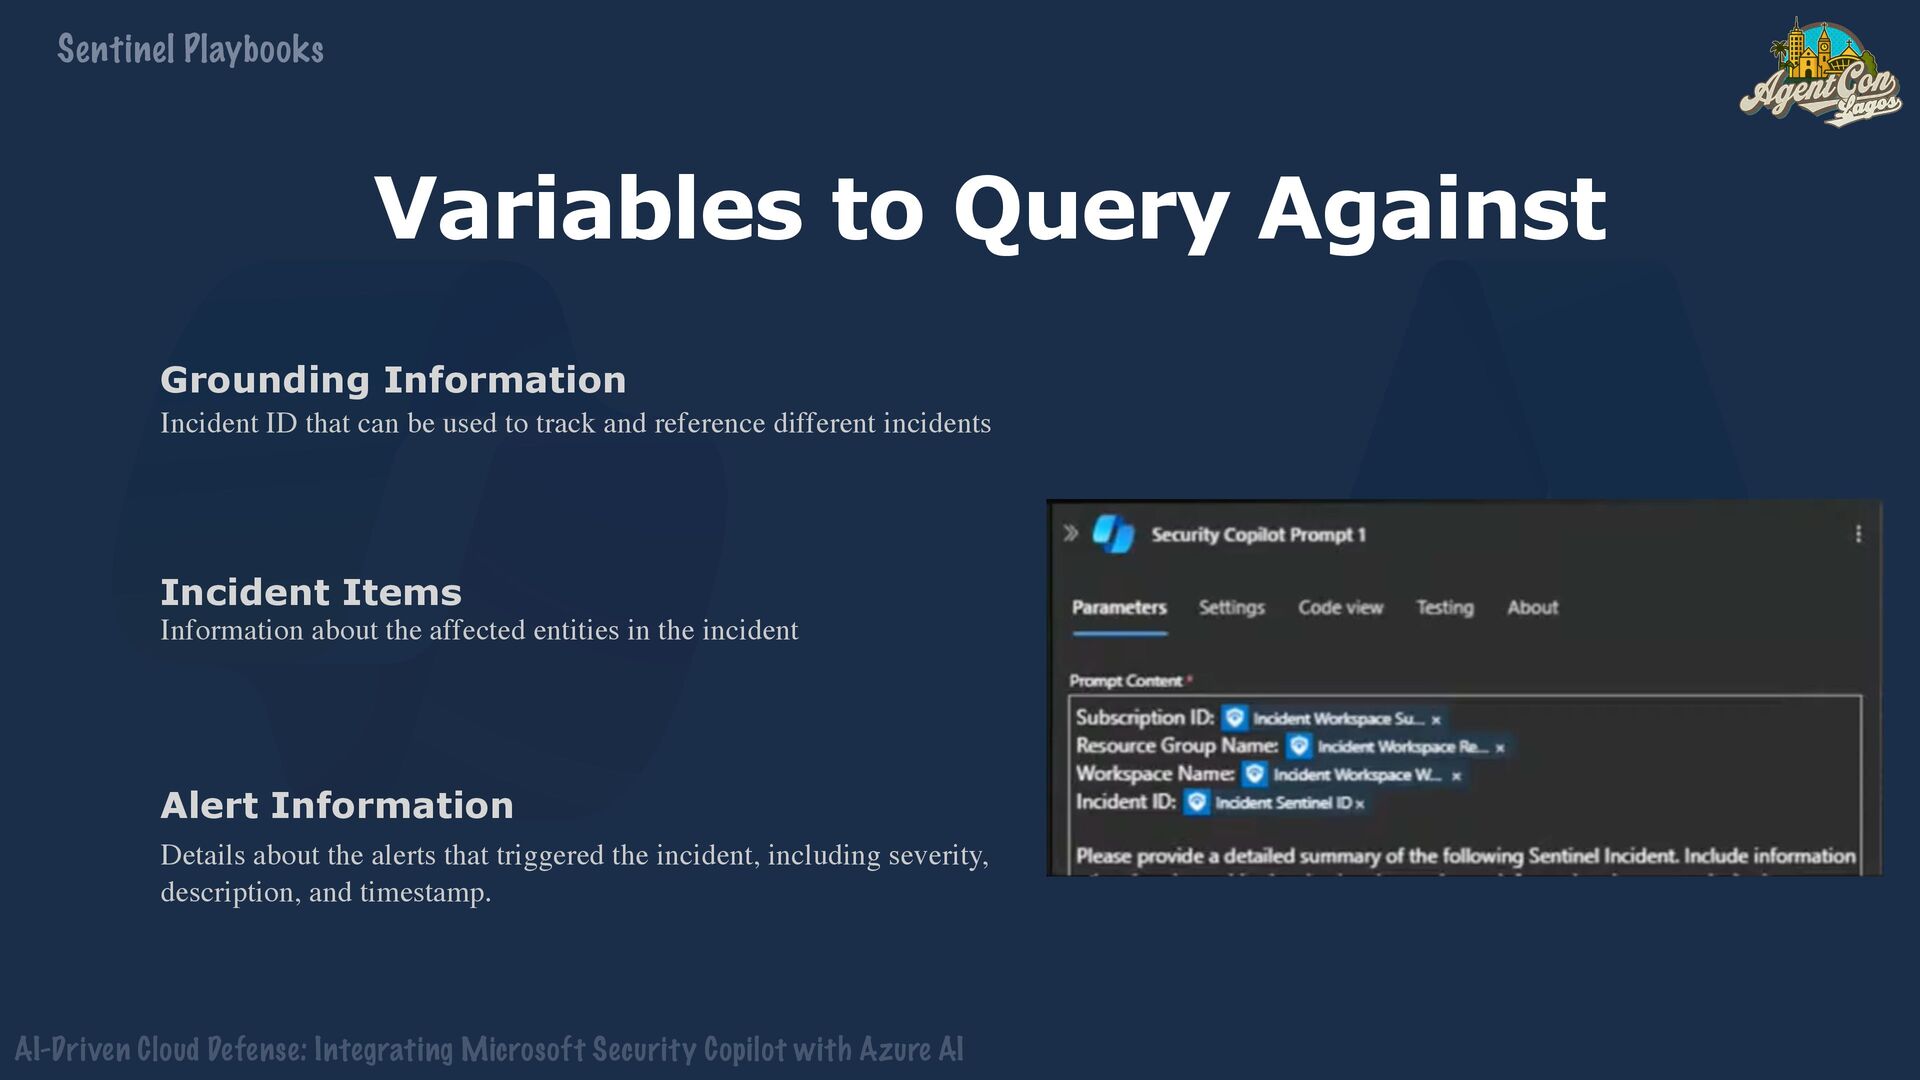
    AI Sentinel Playbooks Variables to Query Against Grounding Information Incident ID that can be used to track and reference different incidents Incident Items Information about the affected entities in the incident Alert Information Details about the alerts that triggered the incident, including severity, description, and timestamp.
  41. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

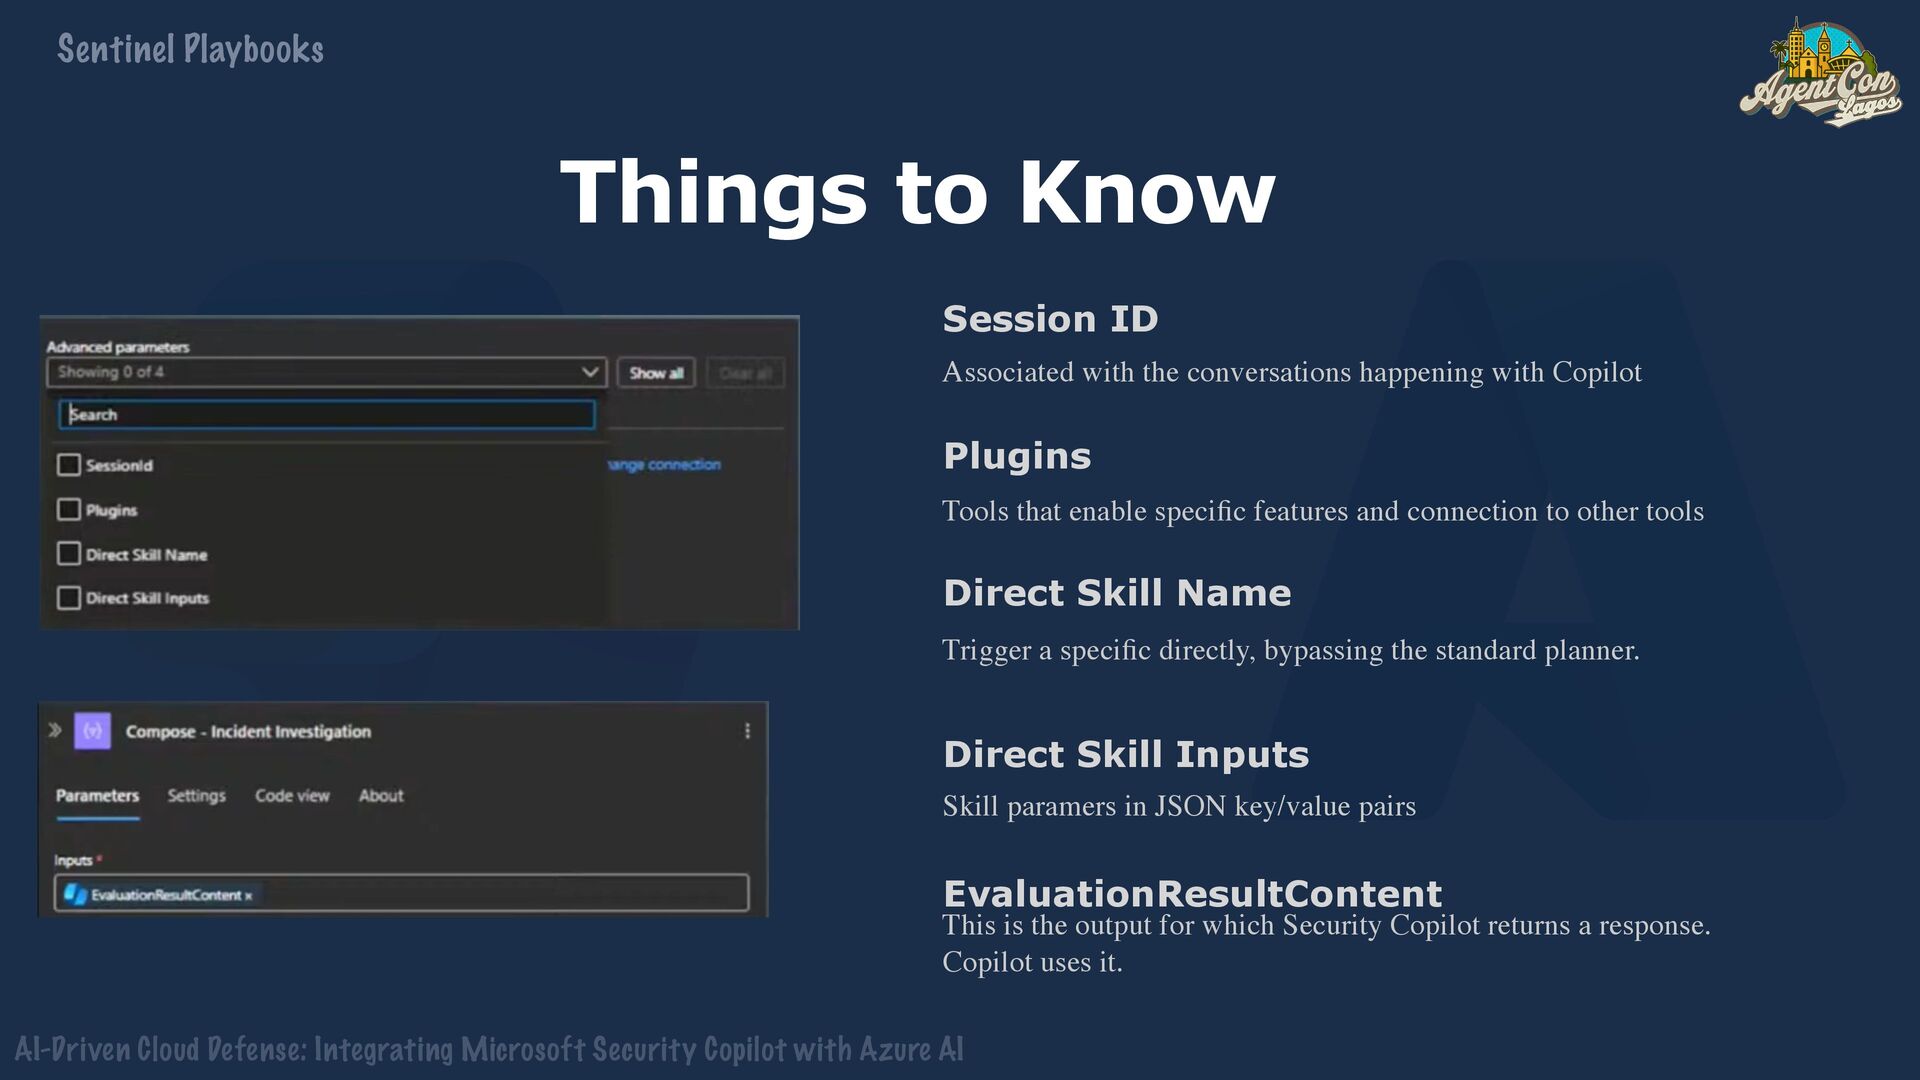
    AI Sentinel Playbooks Things to Know Session ID Associated with the conversations happening with Copilot Plugins Tools that enable speci fi c features and connection to other tools Direct Skill Name Trigger a speci fi c directly, bypassing the standard planner. Direct Skill Inputs Skill paramers in JSON key/value pairs EvaluationResultContent This is the output for which Security Copilot returns a response. Copilot uses it.
  42. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

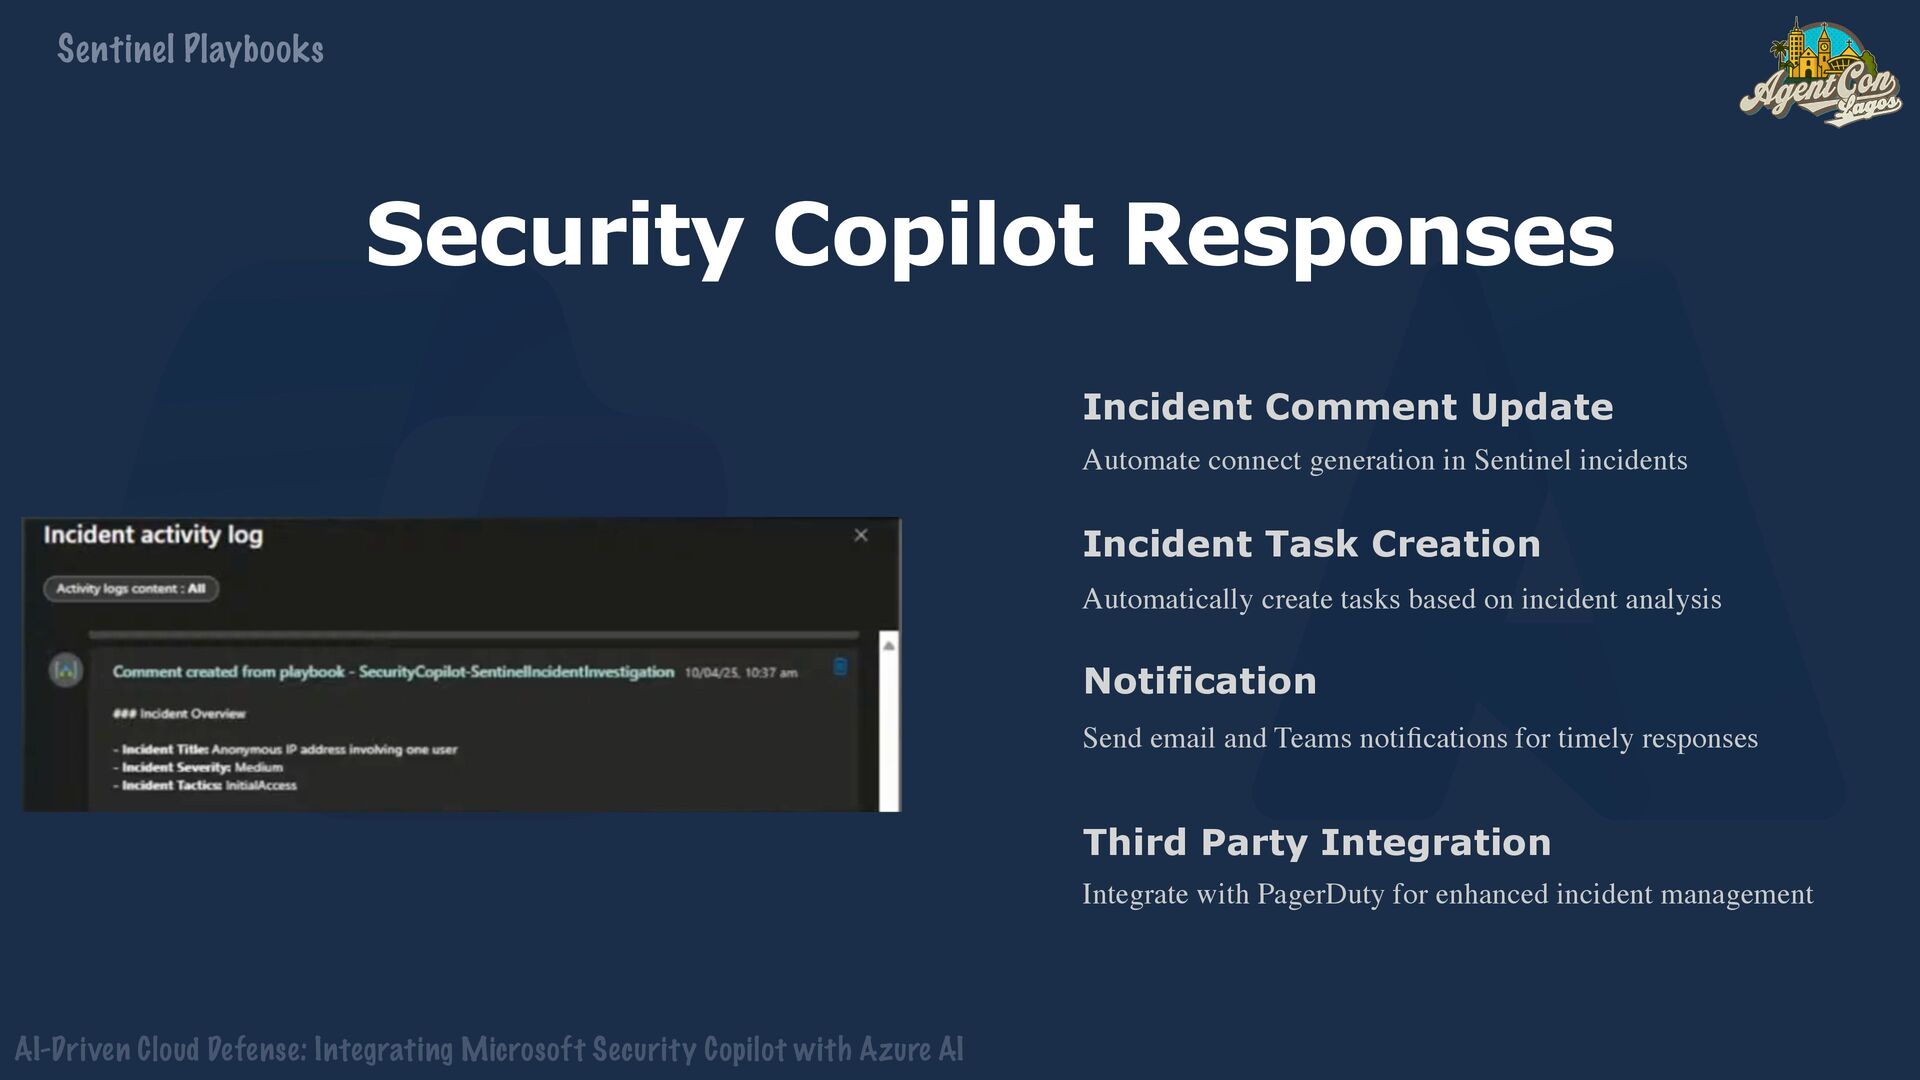
    AI Sentinel Playbooks Security Copilot Responses Incident Comment Update Automate connect generation in Sentinel incidents Incident Task Creation Automatically create tasks based on incident analysis Notification Send email and Teams noti fi cations for timely responses Third Party Integration Integrate with PagerDuty for enhanced incident management
  43. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

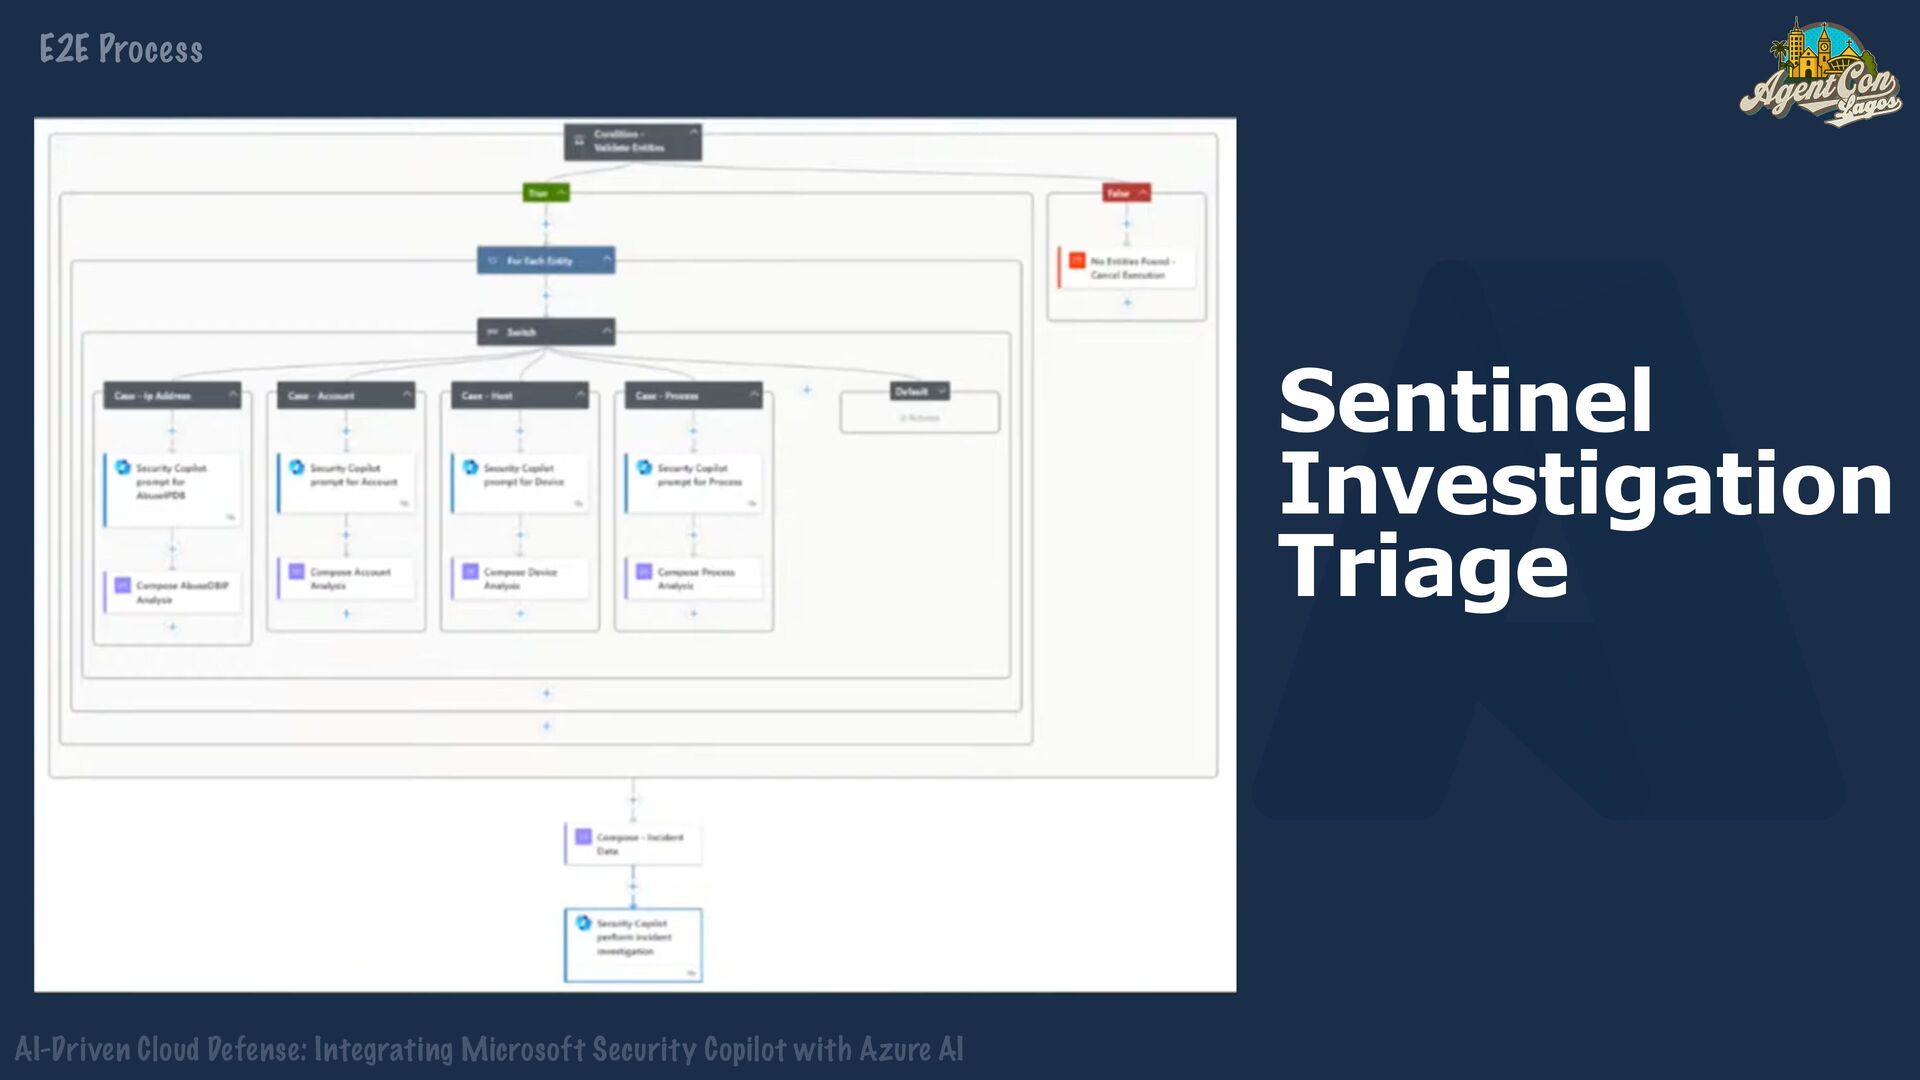
    AI When to Automate Incident Triage Analyze and classify incidents by severity/type. Enrich data with threat intelligence and reputation scores. Alert Enrichment Integrate external sources(e.g, AbuselPDB). Analyze command line elements and processes Automated Response Trigger containment actions. Update incident comments in real-time. Task Automation Auto-create and assign tasks based on analysis. Streamline routine invesigation steps. Third Party Integration Integrate with toools for enhanced management. Sentinel Playbooks
  44. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

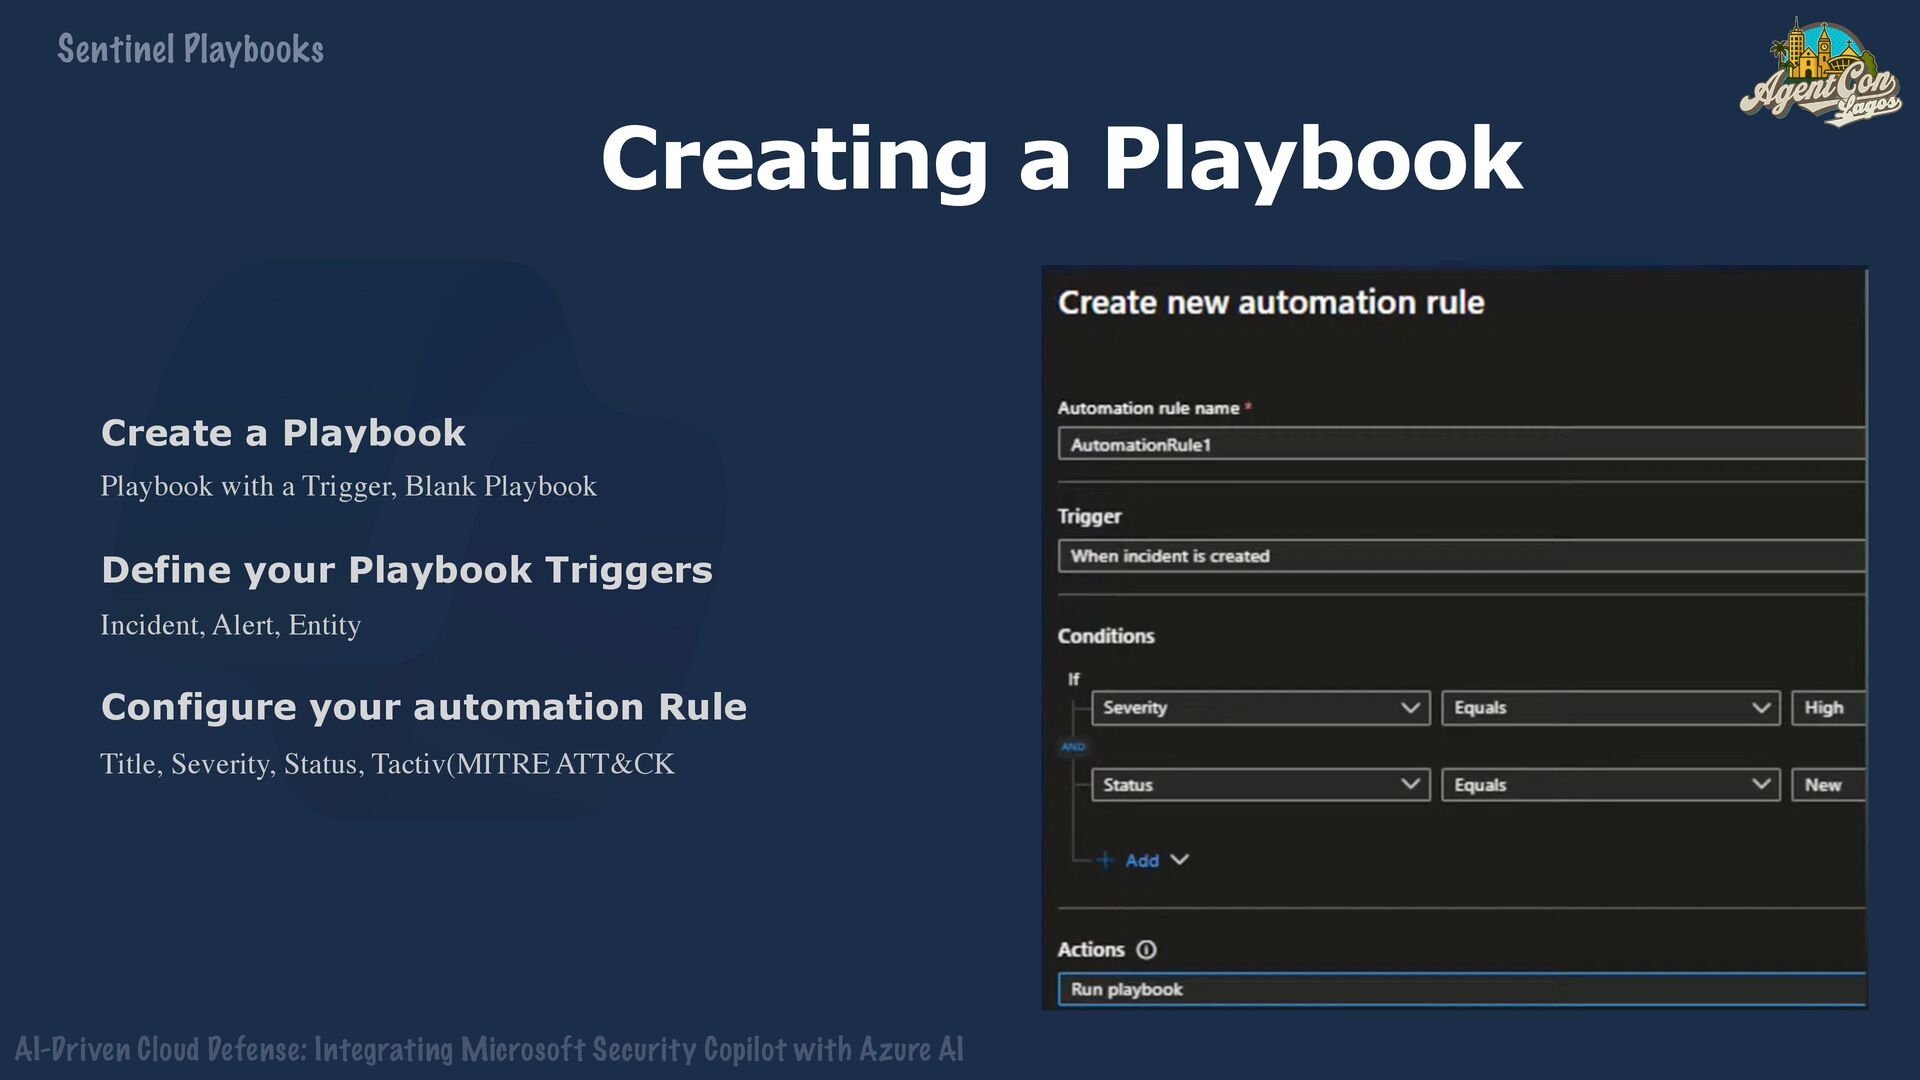
    AI Creating a Playbook Sentinel Playbooks Create a Playbook Playbook with a Trigger, Blank Playbook Define your Playbook Triggers Incident, Alert, Entity Configure your automation Rule Title, Severity, Status, Tactiv(MITRE ATT&CK
  45. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

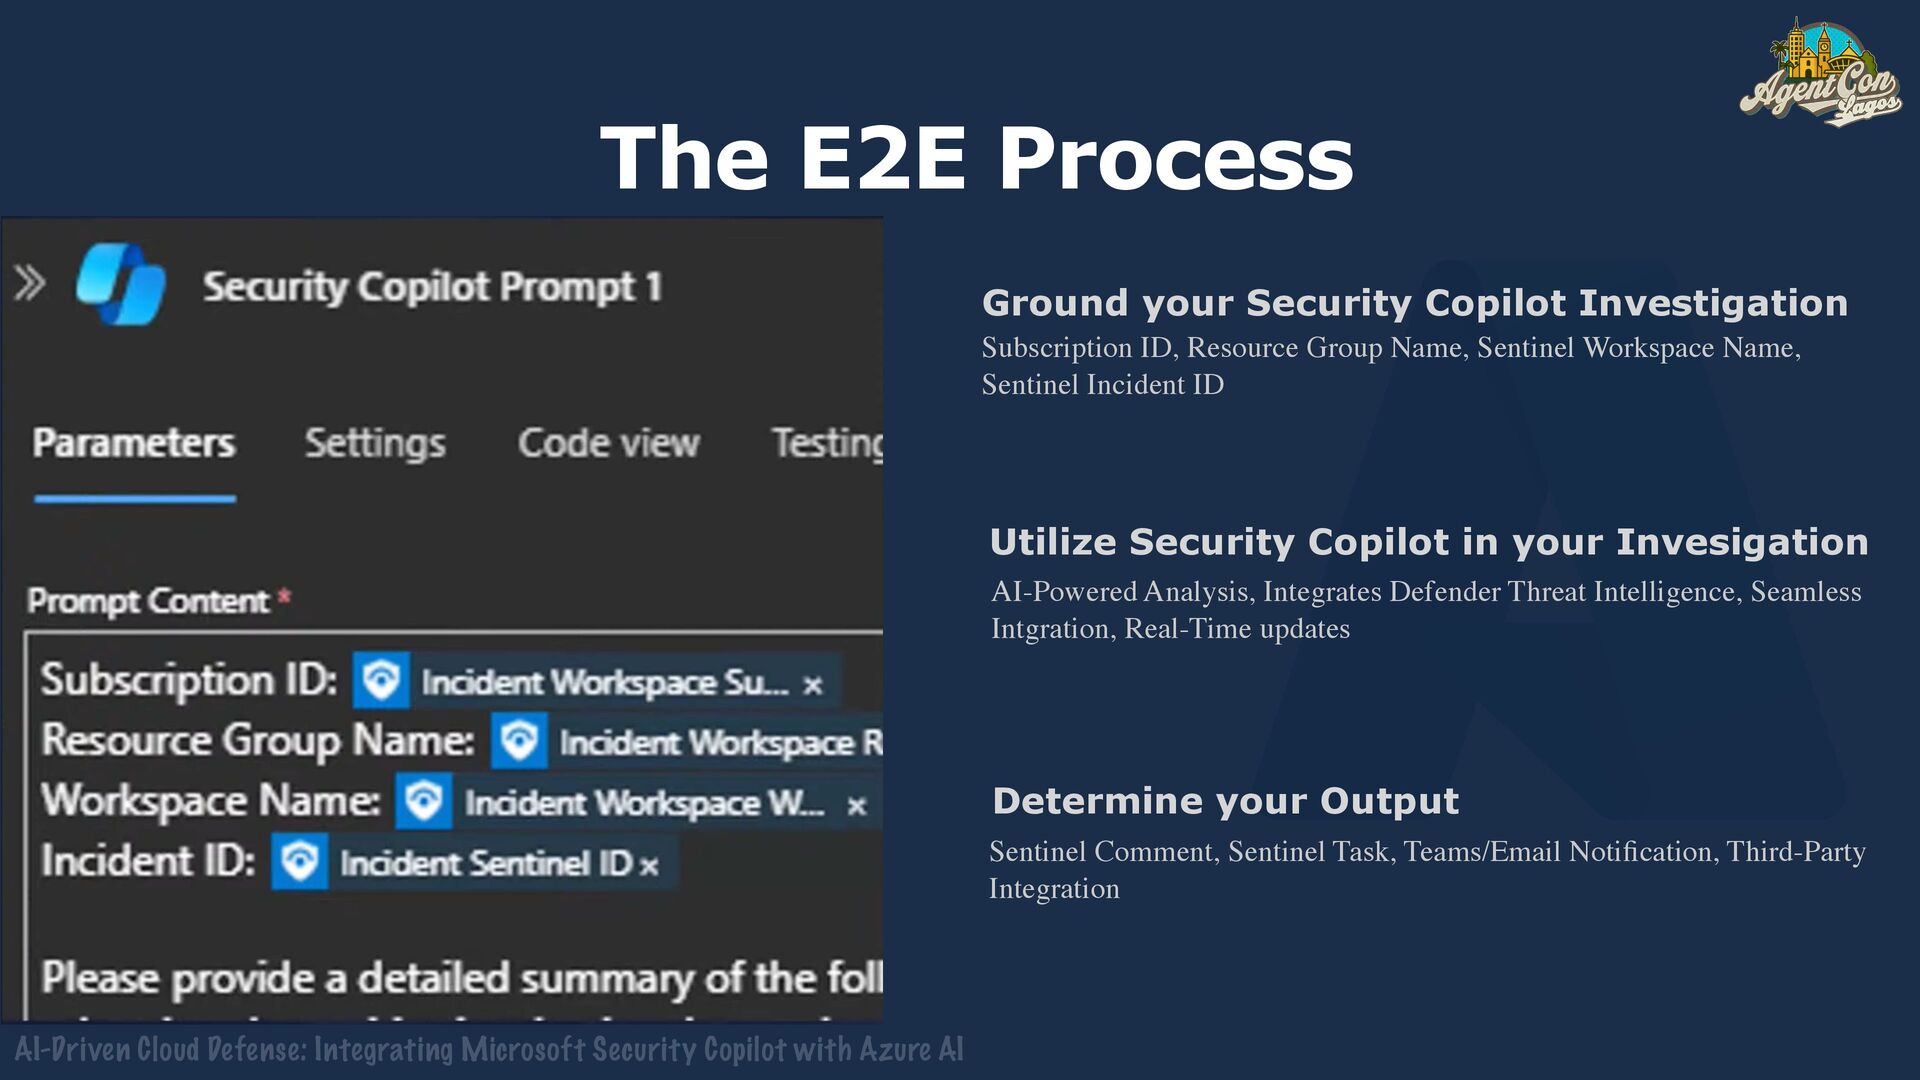
    AI The E2E Process Ground your Security Copilot Investigation Subscription ID, Resource Group Name, Sentinel Workspace Name, Sentinel Incident ID Utilize Security Copilot in your Invesigation AI-Powered Analysis, Integrates Defender Threat Intelligence, Seamless Intgration, Real-Time updates Determine your Output Sentinel Comment, Sentinel Task, Teams/Email Noti fi cation, Third-Party Integration
  46. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

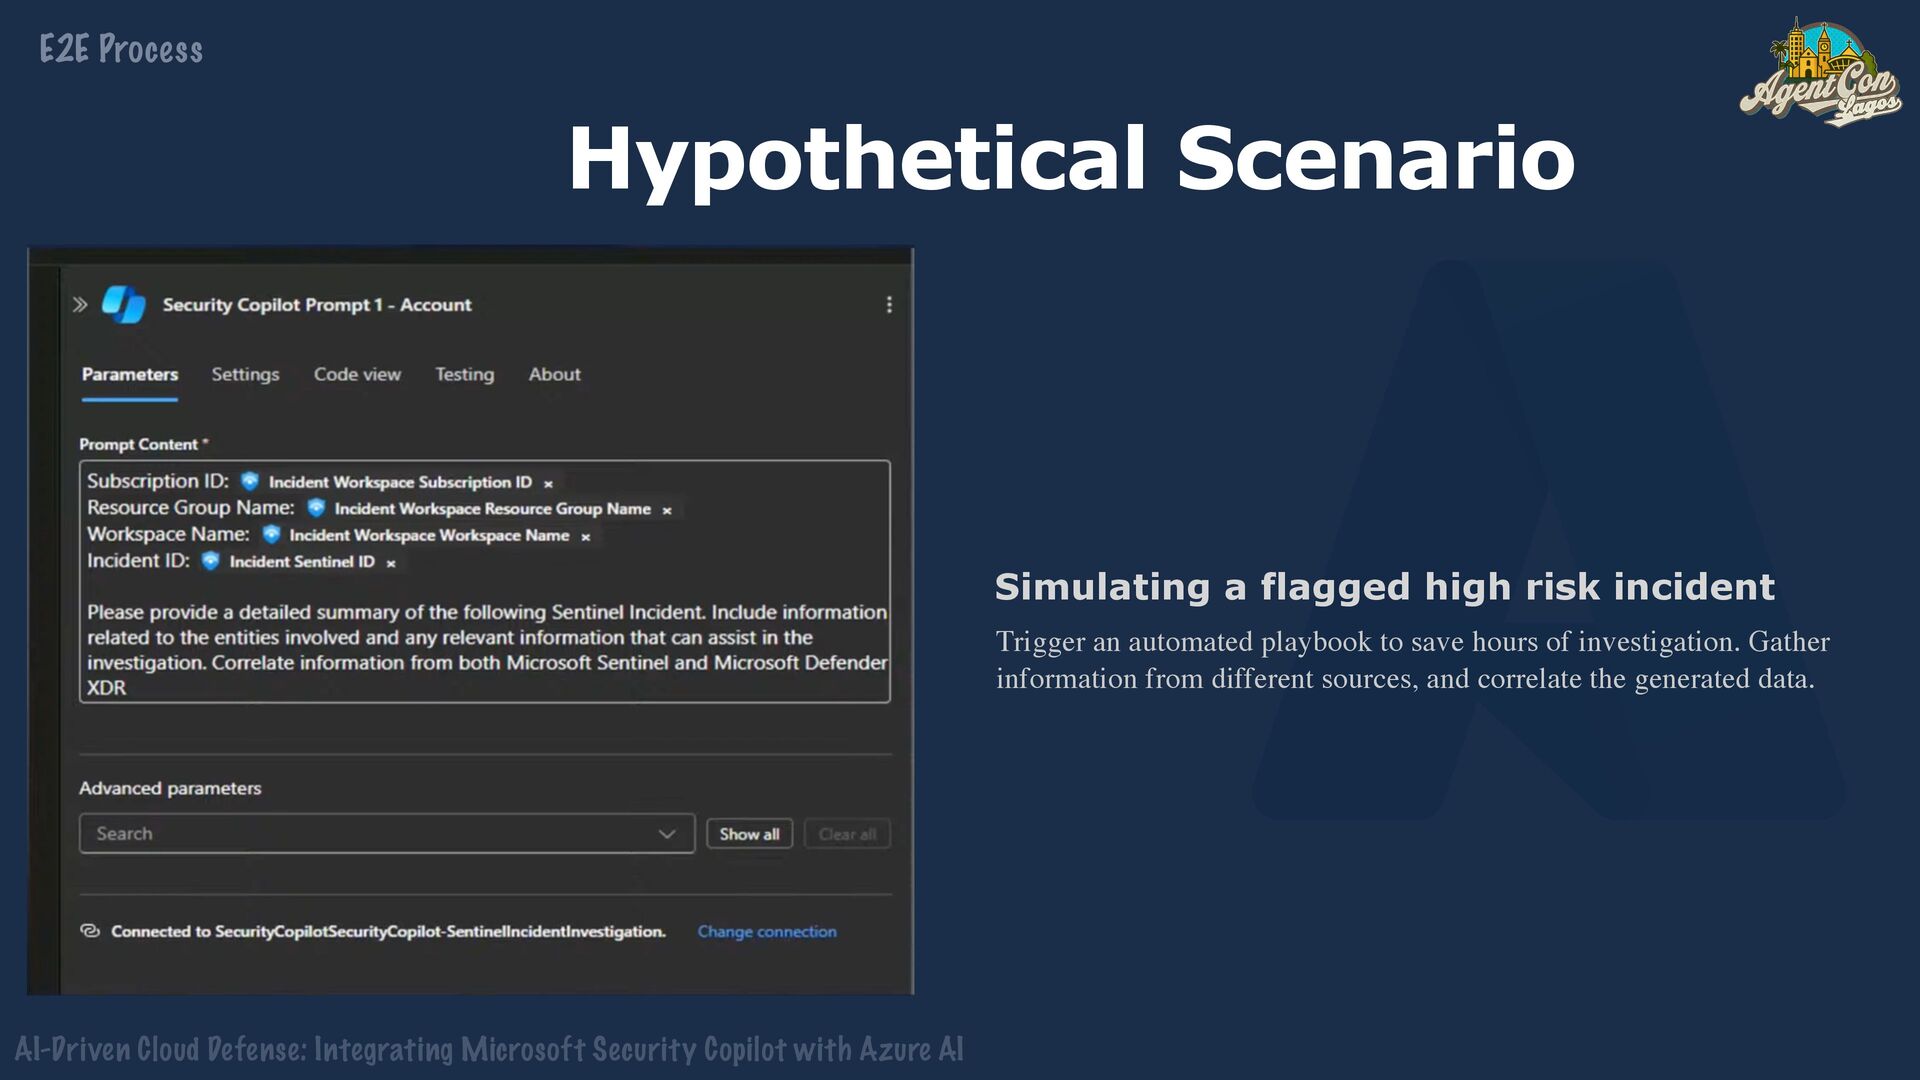
    AI Hypothetical Scenario E2E Process Simulating a flagged high risk incident Trigger an automated playbook to save hours of investigation. Gather information from different sources, and correlate the generated data.
  47. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

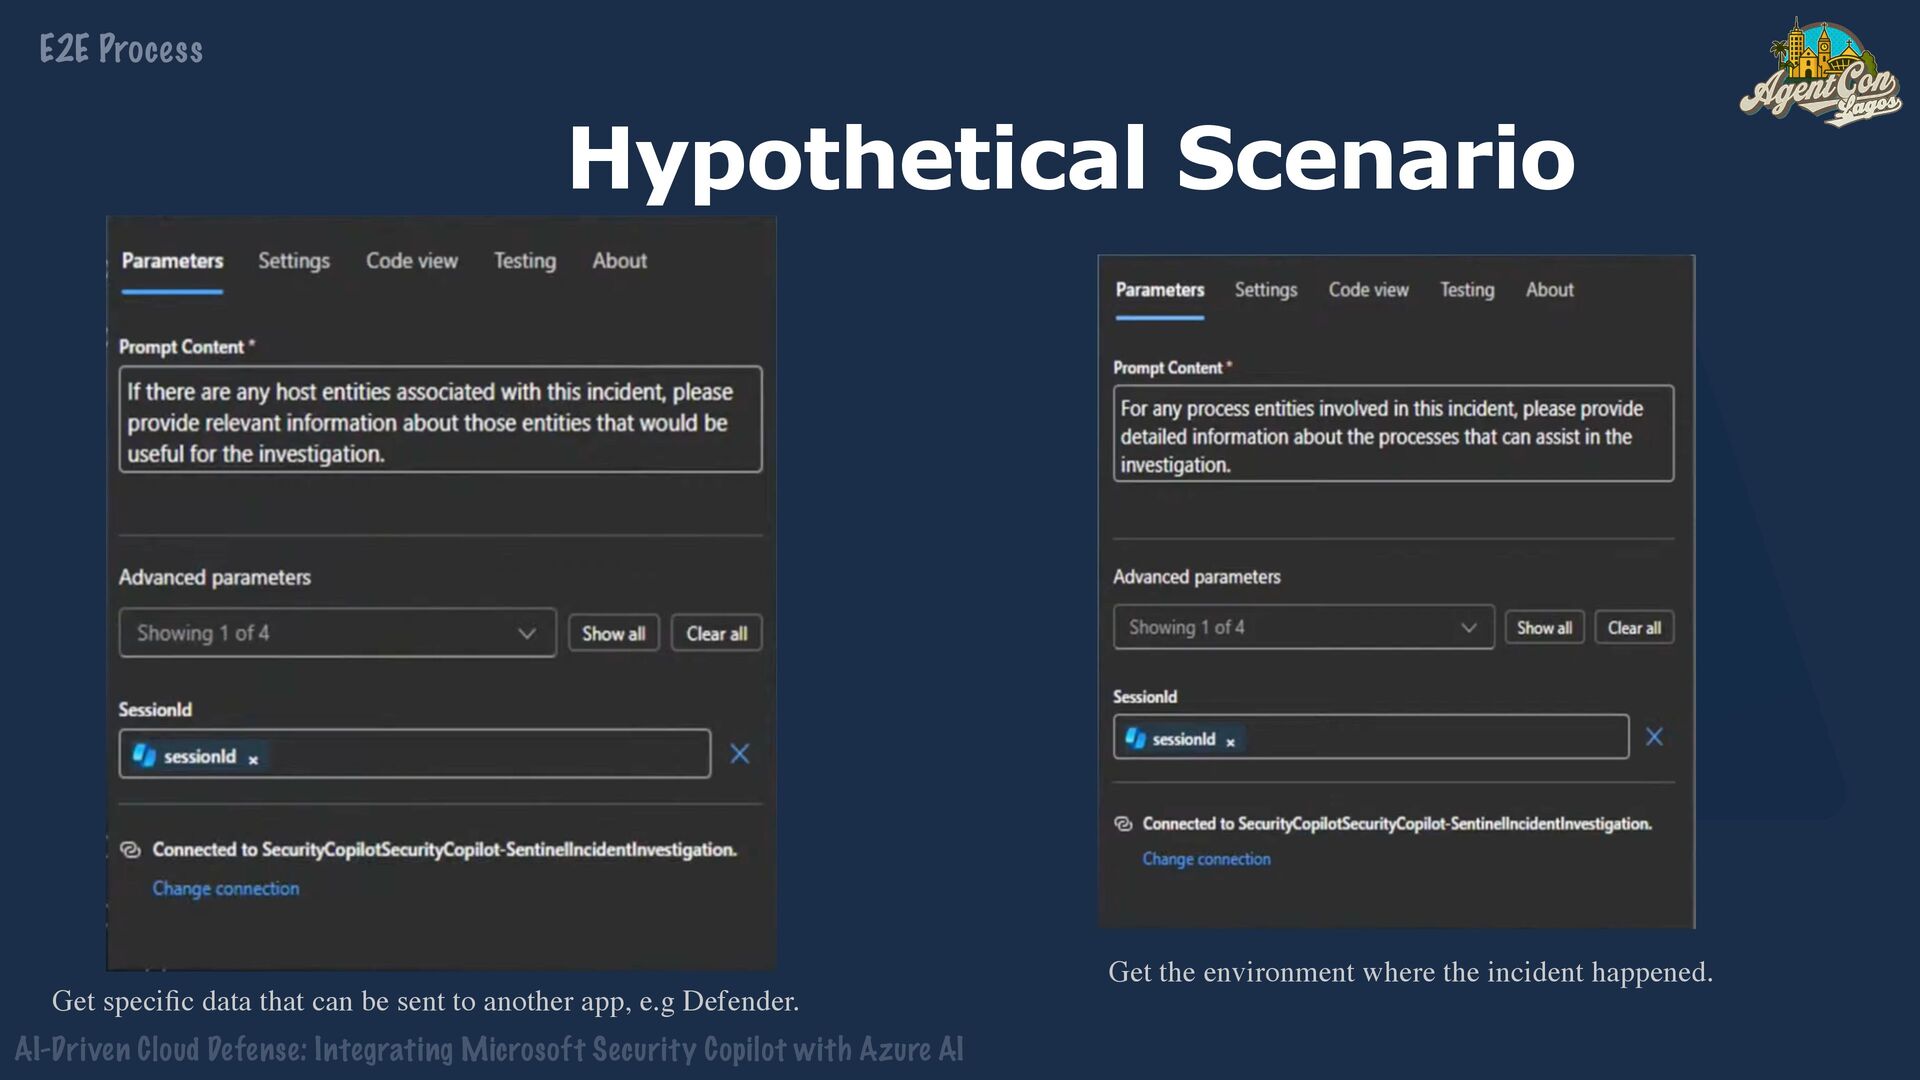
    AI Hypothetical Scenario E2E Process Get the environment where the incident happened. Get speci fi c data that can be sent to another app, e.g Defender.
  48. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

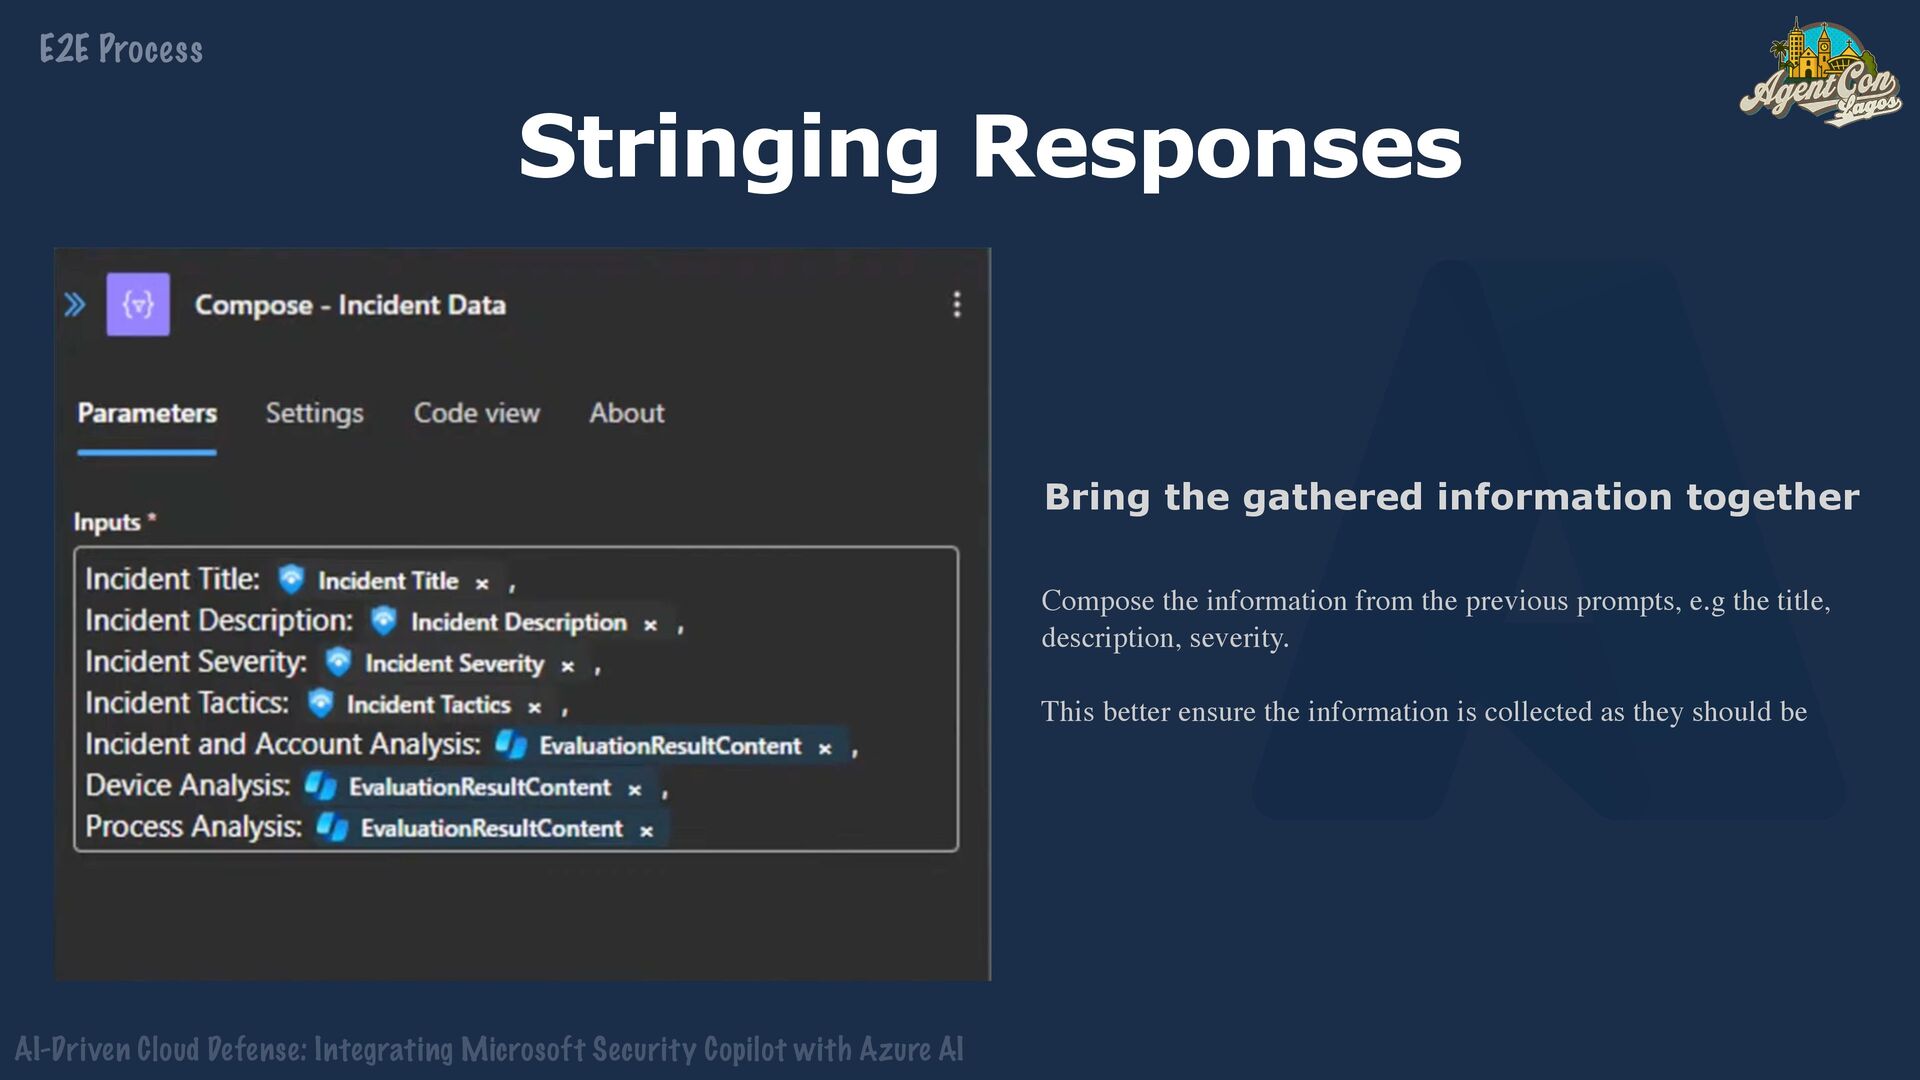
    AI Stringing Responses Bring the gathered information together Compose the information from the previous prompts, e.g the title, description, severity. This better ensure the information is collected as they should be E2E Process
  49. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

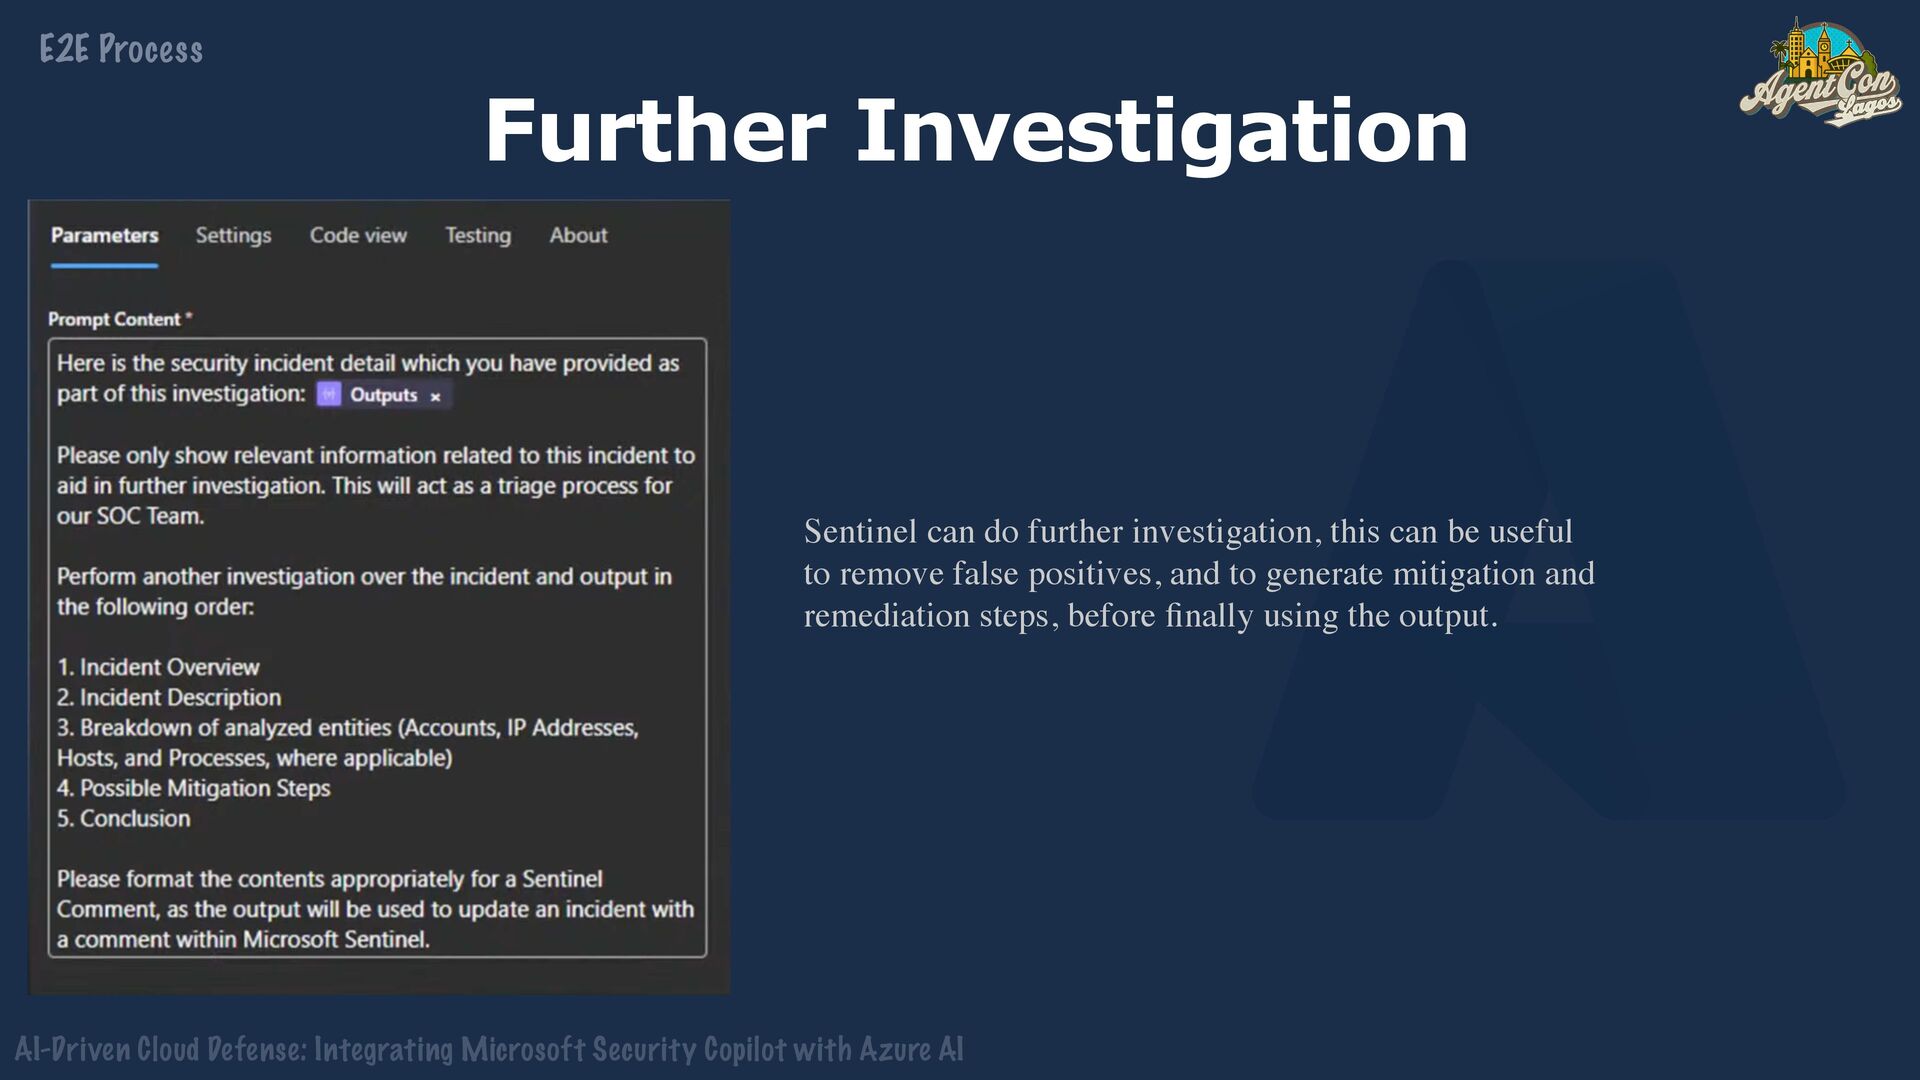
    AI Further Investigation E2E Process Sentinel can do further investigation, this can be useful to remove false positives, and to generate mitigation and remediation steps, before fi nally using the output.
  50. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

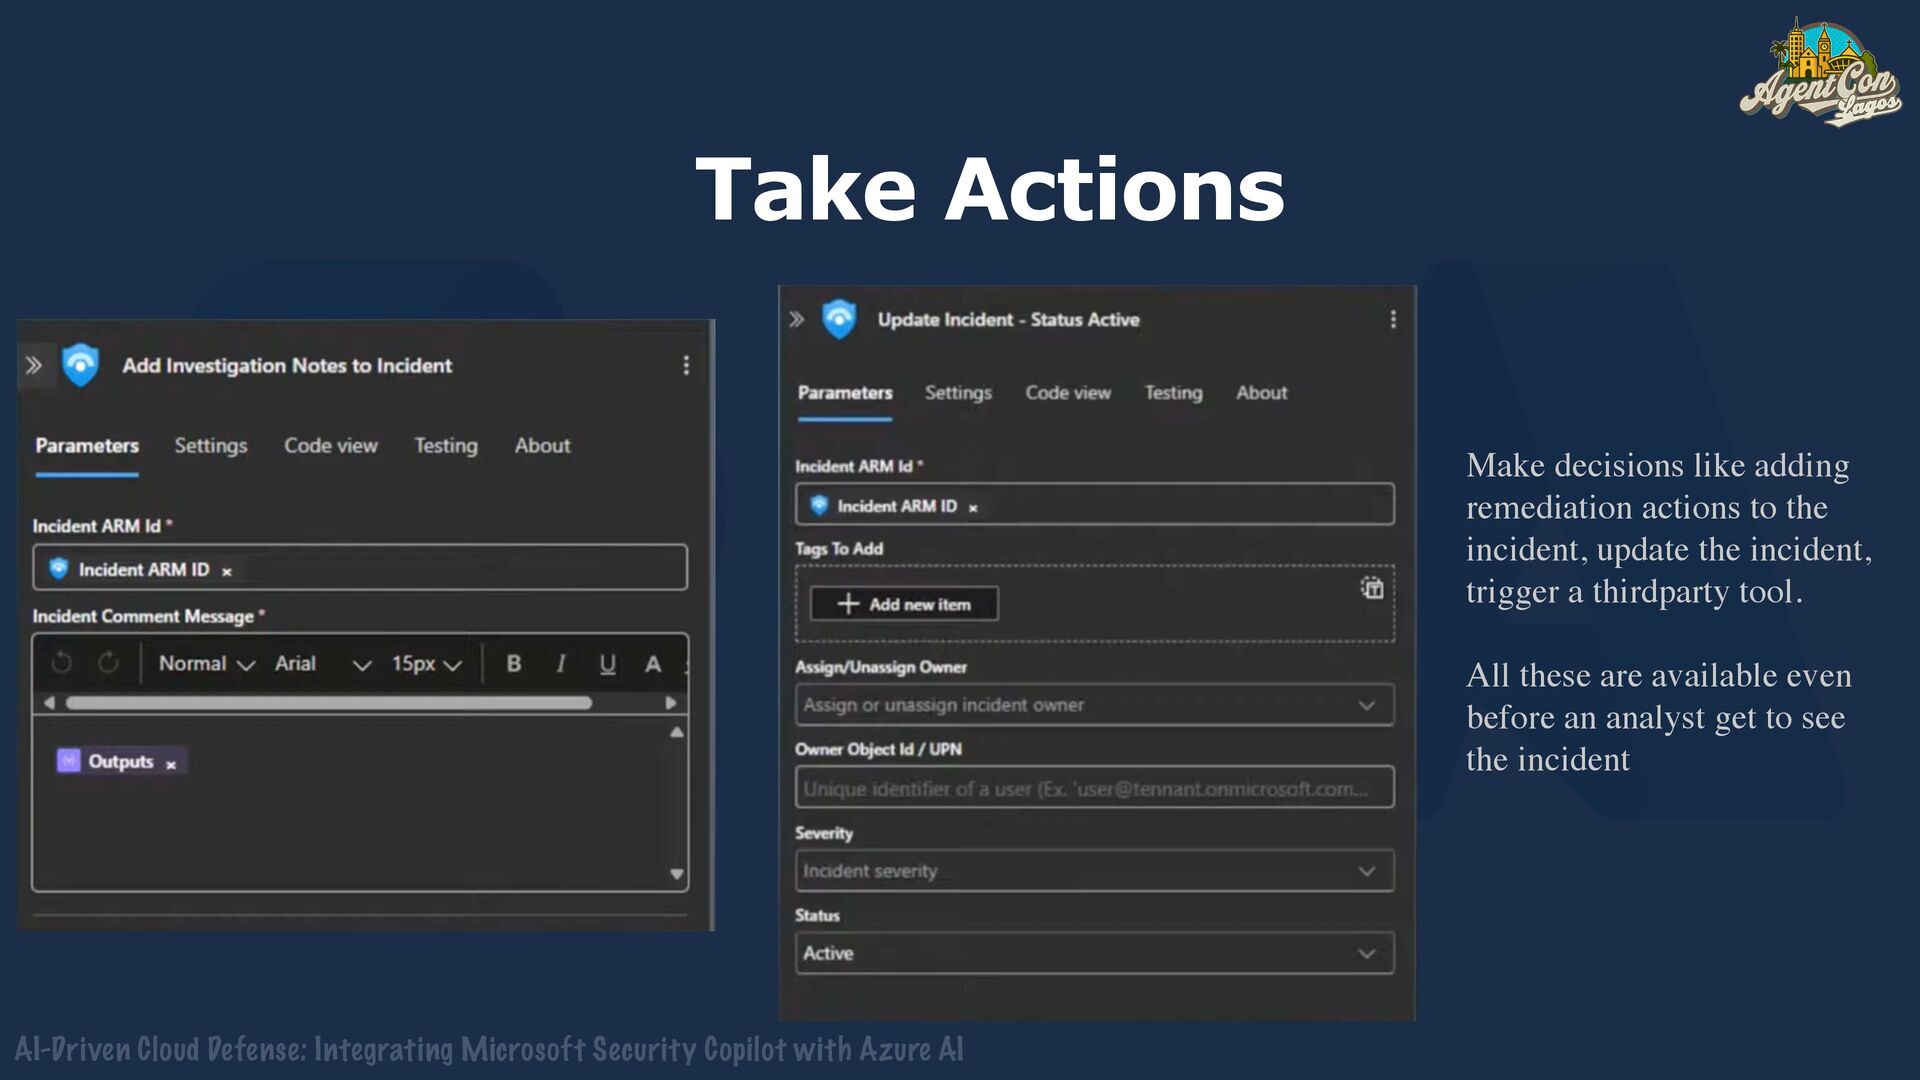
    AI Take Actions Make decisions like adding remediation actions to the incident, update the incident, trigger a thirdparty tool. All these are available even before an analyst get to see the incident
  51. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Automation Outcomes Reduced Mean Time to Detect (MTTD) Reduced Mean Time to Response (MTTR) Increased analyst Efficiency
  52. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI “AI won’t replace analysts — analysts using AI will replace those who don’t.”
  53. + AI-Driven Cloud Defense: Integrating Microsoft Security Copilot with Azure

    AI Aleem Isiaka Software Engineer x.com/limistah github.com/limistah limistah.dev linkedin.com/in/limistah Thank You…