Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
iOS malware: myth or reality?
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
Julien Bachmann
June 08, 2016
Technology
1.4k
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
iOS malware: myth or reality?
talk given at Security B-Sides London
Julien Bachmann
June 08, 2016
More Decks by Julien Bachmann
See All by Julien Bachmann
Advanced exploitation on Linux: ROP and infoleaks
milkmix
3
3.8k
Elasticsearch: incident detection use-cases and security best practices
milkmix
1
1.4k
Using Z3 to solve crackme
milkmix
0
2.1k
Software exploitation : ROP
milkmix
2
600
Clusis Campus 2015 : introduction to Suricata IDS
milkmix
0
310
String format exploitation in 15"
milkmix
1
370
Reversing iOS/OSX malware : wirelurker
milkmix
1
420
import-module IncidentResponse
milkmix
0
160
iOS applications auditing
milkmix
0
180
Other Decks in Technology
See All in Technology
俺の仕事は AIに奪われないし、たぶんその BIも要らない
hikaruri
0
500
すぐできる衛星通信対応 あとは山奥に行くだけ
tatetate55
0
130
10Xに技術的負債をもたらした「2つの境界の歪み」その構造と解消への営み
10xinc
0
2k
生成AIエージェントを用いた、 手動テスト手順書から自動テストへの 変換手法の検討
magicpod
0
160
Cloudflare Workers 向けアプリを C# で構築する ~WASM Native AOT への道~
nenonaninu
0
120
顧客に向き合う開発組織へ。リアーキテクチャとフィーチャーチーム化で挑む組織改革
safie
0
2k
OpenTelemetry eBPF Instrumentationの舞台裏 / Behind the Scenes of OpenTelemetry eBPF Instrumentation
ymotongpoo
4
1.3k
Claude in Chrome 入門 / Introduction to Claude in Chrome
cielo1985
0
840
ユーザー価値を届け続けるためにウォンテッドリーが大切にしている文化
kotaminato
0
170
アプリログインとWeb認証基盤をつなぐ ASWebAuthenticationSession 作法
shimastripe
1
330
データ_AIの事業の勝敗をわけるもの
nek0128
1
420
【技術的負債conf】事業成長に伴う技術的負債の説明責任とAIによるモニタリング、認知的負債について
i35_267
3
1.7k
Featured
See All Featured
Visualization
eitanlees
152
17k
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
How to Think Like a Performance Engineer
csswizardry
28
2.8k
Amusing Abliteration
ianozsvald
1
300
16th Malabo Montpellier Forum Presentation
akademiya2063
PRO
0
380
Marketing Yourself as an Engineer | Alaka | Gurzu
gurzu
0
300
Docker and Python
trallard
47
4.2k
How to Ace a Technical Interview
jacobian
281
24k
The AI Search Optimization Roadmap by Aleyda Solis
aleyda
1
6.2k
Rails Girls Zürich Keynote
gr2m
96
14k
Gemini Prompt Engineering: Practical Techniques for Tangible AI Outcomes
mfonobong
2
530
個人開発の失敗を避けるイケてる考え方 / tips for indie hackers
panda_program
123
22k
Transcript
C O N F I D E N T I
A L ©2016 KUDELSKI GROUP / All rights reserved. iOS MALWARE : MYTH OR REALITY? Julien Bachmann @milkmix_
INTRODUCTION
C O N F I D E N T I
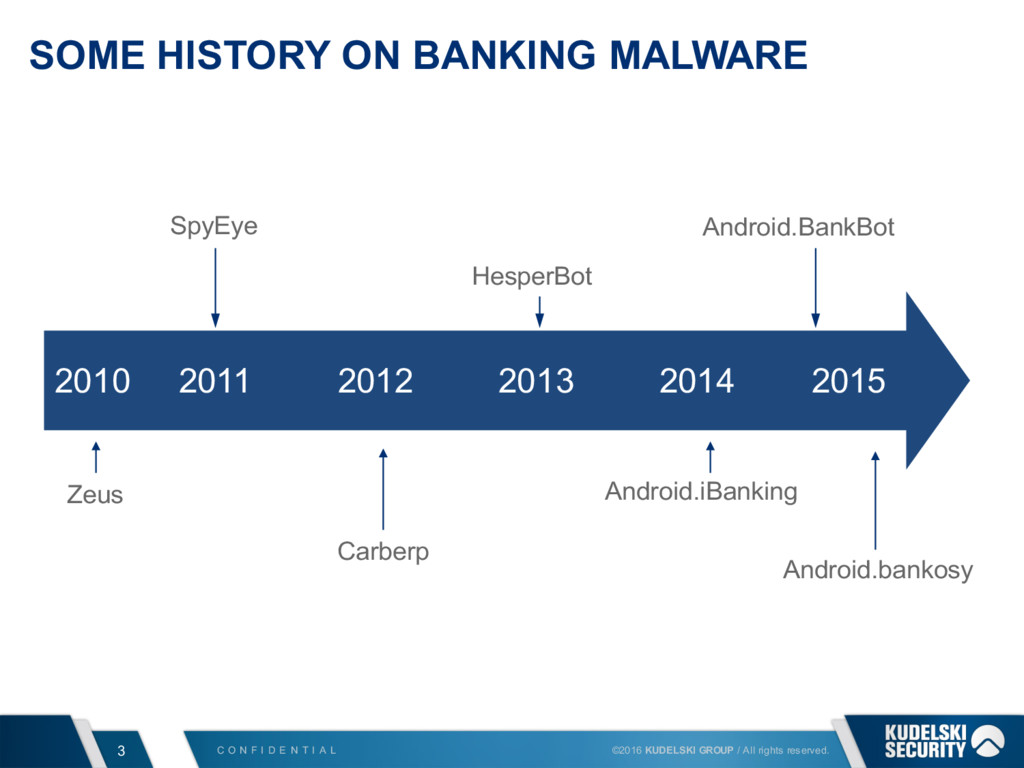
A L 3 ©2016 KUDELSKI GROUP / All rights reserved. 2010 2011 2012 2013 2014 2015 SOME HISTORY ON BANKING MALWARE Zeus SpyEye Carberp HesperBot Android.iBanking Android.BankBot Android.bankosy
C O N F I D E N T I
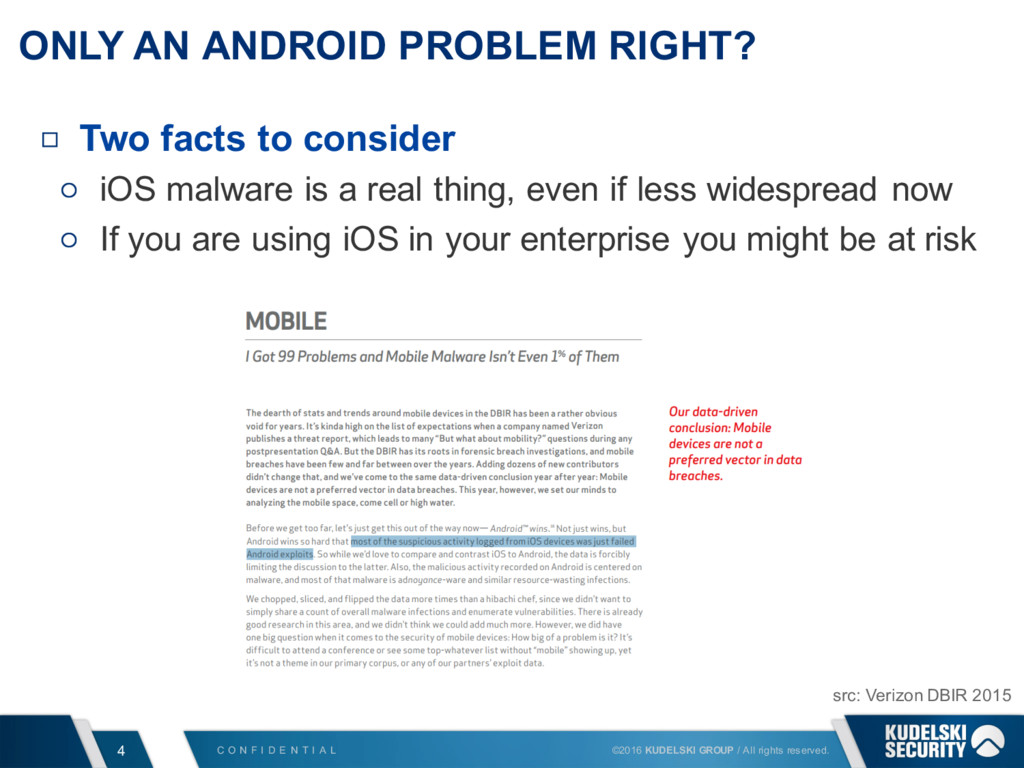
A L 4 ©2016 KUDELSKI GROUP / All rights reserved. ONLY AN ANDROID PROBLEM RIGHT? Two facts to consider iOS malware is a real thing, even if less widespread now If you are using iOS in your enterprise you might be at risk src: Verizon DBIR 2015
C O N F I D E N T I
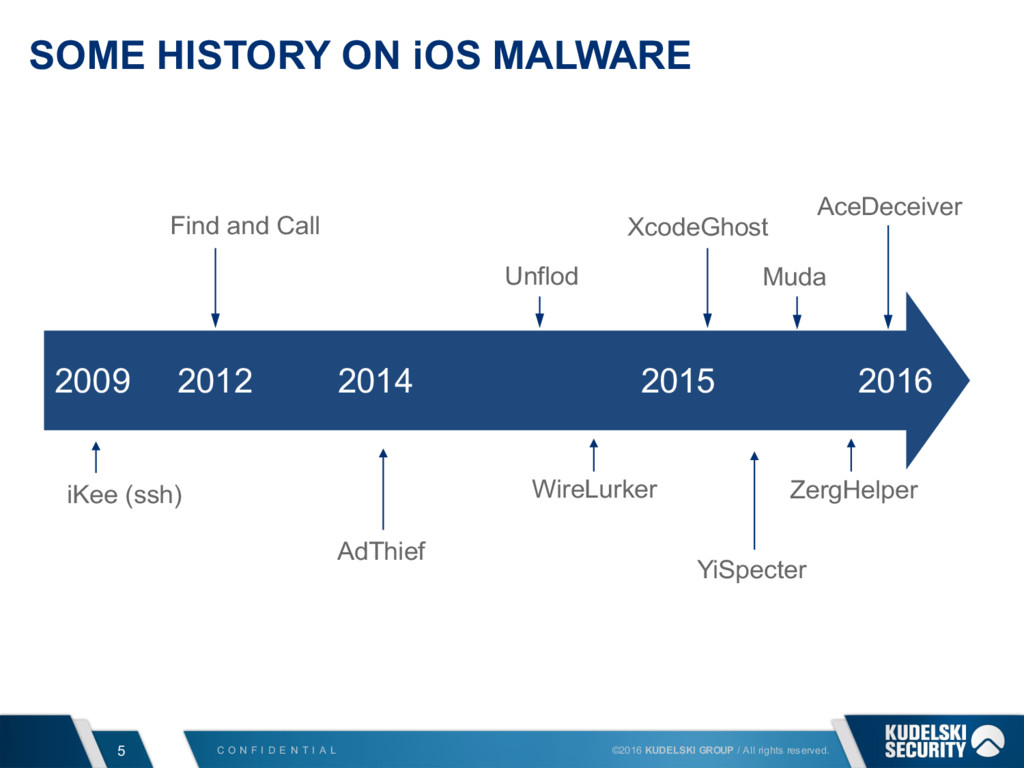
A L 5 ©2016 KUDELSKI GROUP / All rights reserved. 2009 2012 2014 2015 2016 SOME HISTORY ON iOS MALWARE iKee (ssh) Find and Call AdThief Unflod WireLurker XcodeGhost YiSpecter Muda ZergHelper AceDeceiver
QUICK RECAP ON iOS SECURITY
C O N F I D E N T I
A L 7 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS INSTALLATION Limited number of installation paths Closed platform well restricted by Apple Only authorized methods controlled by Apple on non- jailbroken device
C O N F I D E N T I
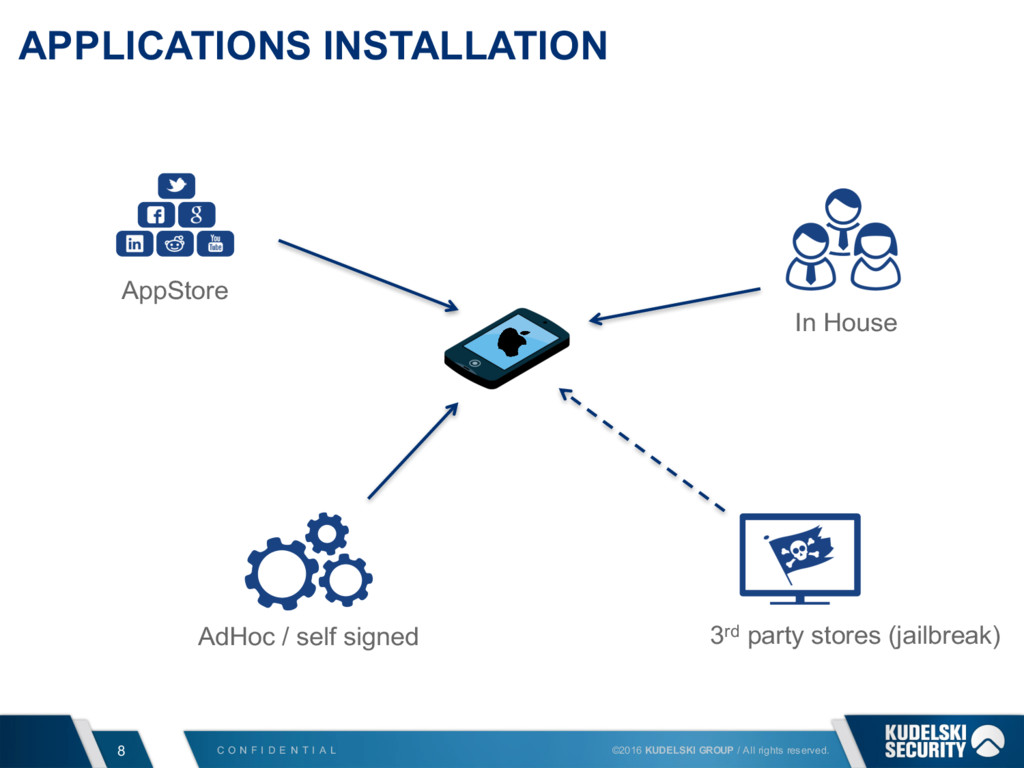
A L 8 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS INSTALLATION AppStore AdHoc / self signed In House 3rd party stores (jailbreak)
C O N F I D E N T I
A L 9 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS INSTALLATION AppStore Require Developer certificate Applications are reviewed In House Common method for enterprise applications Require Enterprise Developer account Require Provisioning profile installed on device Ad Hoc Used during development Limited to 100 devices with provisioned UDID Self signed New with iOS 9 and Xcode 7, sign for personal devices
C O N F I D E N T I
A L 10 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS INSTALLATION The jailbroken case Several advantages while jailbreaking a device Allows to validate security of applications But disable code signing validations Allows installing applications from untrusted sources
C O N F I D E N T I
A L 11 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS RESTRICTIONS Limitations put in place by Apple Applications running in a sandbox Seat-Belt Limited access to filesystem and resources Applications are isolated from one another Requested accesses validated on the AppStore Some limitations may apply…
C O N F I D E N T I
A L 12 ©2016 KUDELSKI GROUP / All rights reserved. HOW DEVICES ARE INFECTED? Mostly phishing Lure users into installing malicious application Download link in emails / messages Used it before in phishing campaign for customer : ~10% No exploits and watering hole? Exploitation of software vulnerabilities through the browser Possible but remote code execs are expensive on iOS
C O N F I D E N T I
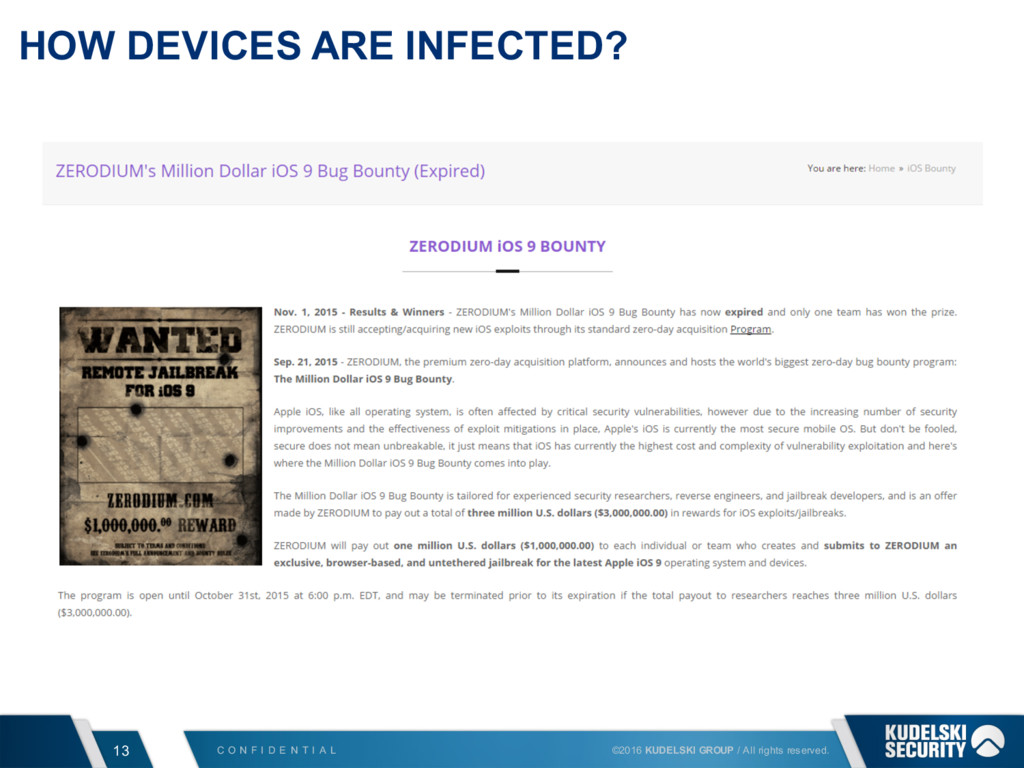
A L 13 ©2016 KUDELSKI GROUP / All rights reserved. HOW DEVICES ARE INFECTED?
C O N F I D E N T I
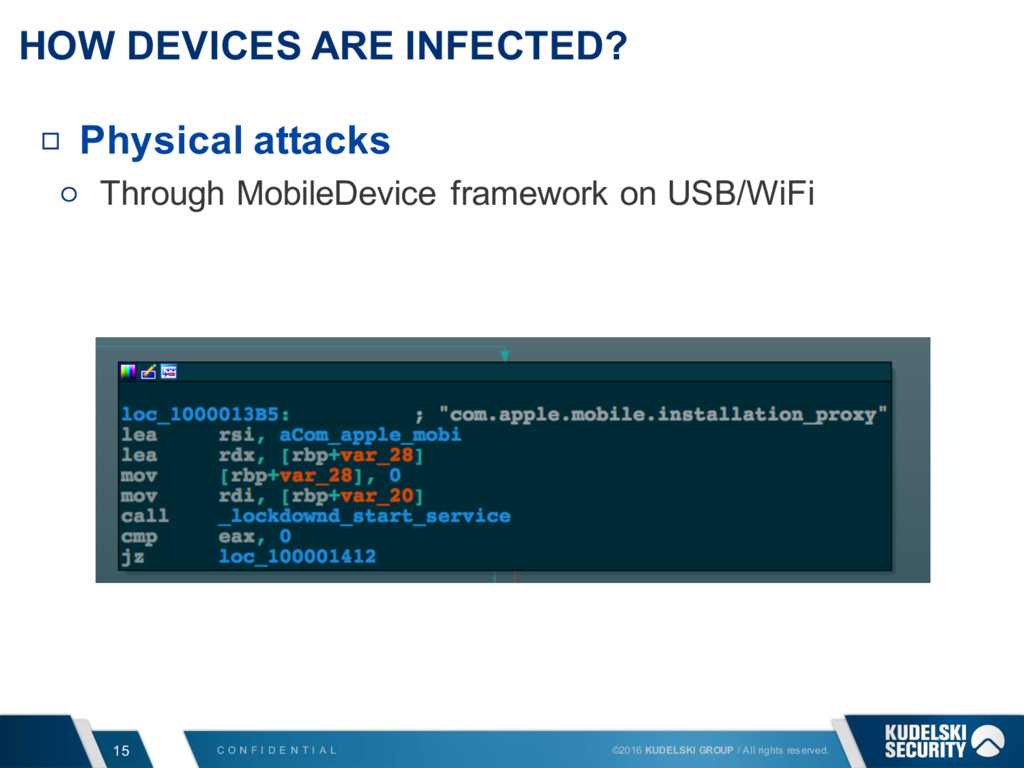
A L 14 ©2016 KUDELSKI GROUP / All rights reserved. HOW DEVICES ARE INFECTED? Traffic injection From the public news, most cases currently in Asia DNS redirects in China Attacks on mobile devices through fake eNodeB Physical attacks Through MobileDevice framework on USB/WiFi AirDrop software flaws Code injection Ex. JSPatch
C O N F I D E N T I
A L 15 ©2016 KUDELSKI GROUP / All rights reserved. HOW DEVICES ARE INFECTED? Physical attacks Through MobileDevice framework on USB/WiFi
C O N F I D E N T I
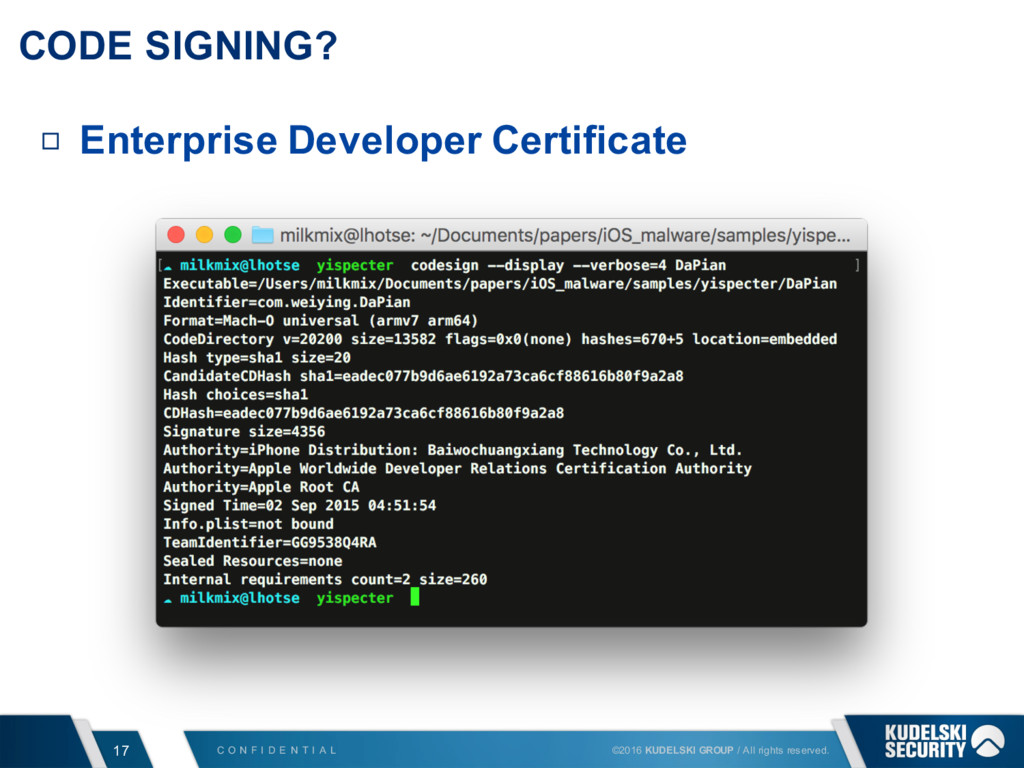
A L 16 ©2016 KUDELSKI GROUP / All rights reserved. CODE SIGNING? Phishing is not enough Code signing still performed by iOS Except on jailbroken devices Ad Hoc Too complicated, requires UDID Leaks in the past years, limited now with Apple restrictions Potentially on very targeted attacks Enterprise Developer Certificate User validation Certificate can be easily revoked by Apple upon detection
C O N F I D E N T I
A L 17 ©2016 KUDELSKI GROUP / All rights reserved. CODE SIGNING? Enterprise Developer Certificate
C O N F I D E N T I
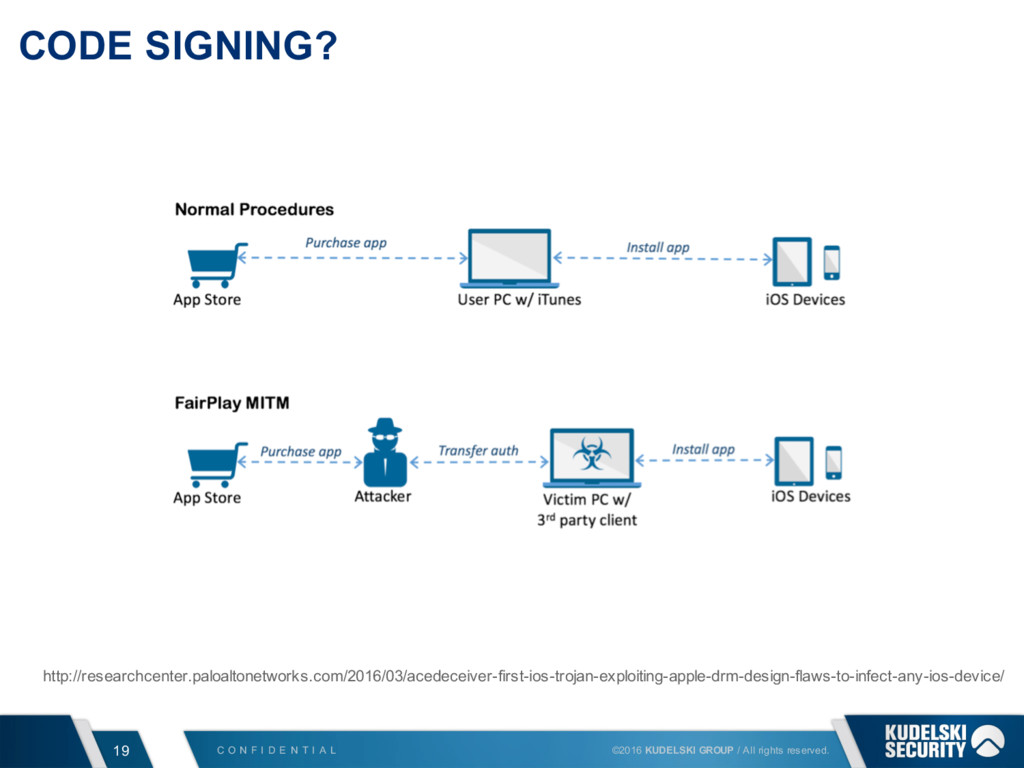
A L 18 ©2016 KUDELSKI GROUP / All rights reserved. CODE SIGNING? Recently in the news “Malware bypassing Apple code signing mechanism” AceDeceiver Truth (explanation w/o the hype) Still requires to be published and accepted by Apple at least once in one of the stores (US, CH, CN, …) Can use geolocation of incoming IP addresses to enable/disable features in the code Possible to exploit design flaw in the validation process when installing from iTunes on Mac/PC Allows to install the malware from Mac/PC even if certificate revoked
C O N F I D E N T I
A L 19 ©2016 KUDELSKI GROUP / All rights reserved. CODE SIGNING? http://researchcenter.paloaltonetworks.com/2016/03/acedeceiver-first-ios-trojan-exploiting-apple-drm-design-flaws-to-infect-any-ios-device/
MALICIOUS ACTIONS
C O N F I D E N T I
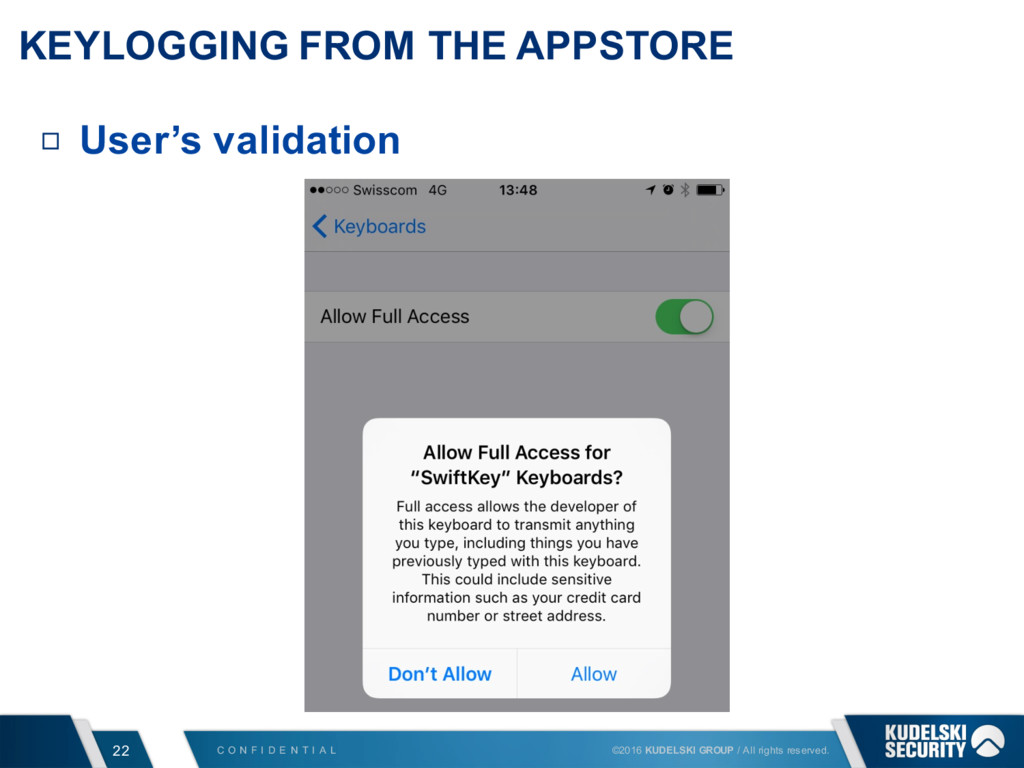
A L 21 ©2016 KUDELSKI GROUP / All rights reserved. APPSTORE PERMISSIONS Audio recording Easily performed through the API When in background applications are preempted by iOS Except if defined as background application Ribbon displayed to the user Keylogging Since iOS8 : extensions (keyboard, browser filtering, …) Isolated from standard application so no access to Internet or files… … except if requested
C O N F I D E N T I
A L 22 ©2016 KUDELSKI GROUP / All rights reserved. KEYLOGGING FROM THE APPSTORE User’s validation
C O N F I D E N T I
A L 23 ©2016 KUDELSKI GROUP / All rights reserved. PRIVATE API In the news
C O N F I D E N T I
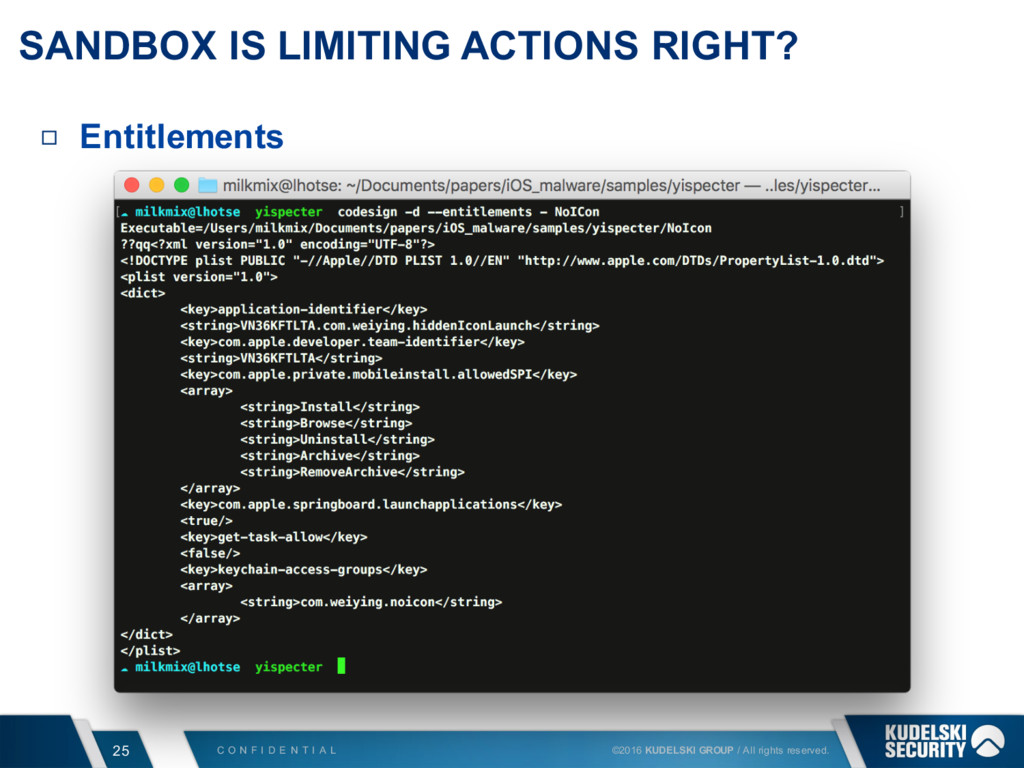
A L 24 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? Entitlements 1. Developers should specify entitlements at compilation • http://newosxbook.com/ent.jl 2. Validated by the AppStore 3. Some additional rights for selected partners 4. Enforced on device by seat-belt Private API Forbidden by Apple in the guidelines Still requires entitlements to access data due to sandbox Does not break applications isolation principle Would require to elevate privileges to do so Or flaws in the private APIs validation mechanism (Stefan Esser app) Difficult to detect with automated analysis (static and dynamic)
C O N F I D E N T I
A L 25 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? Entitlements
C O N F I D E N T I
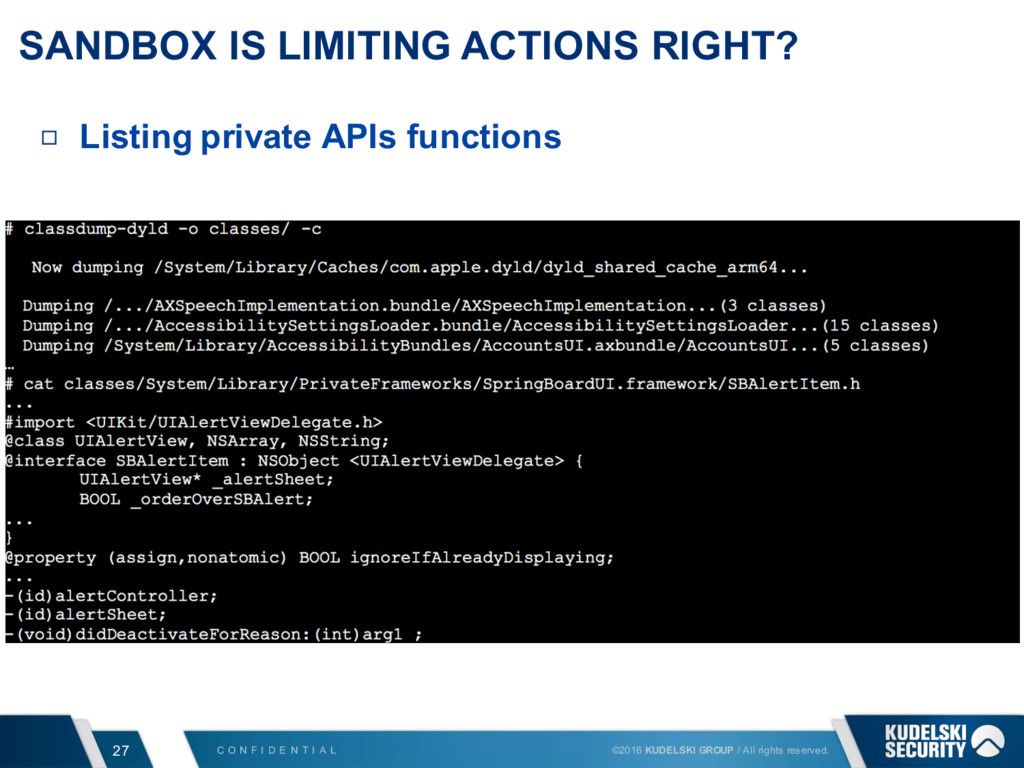
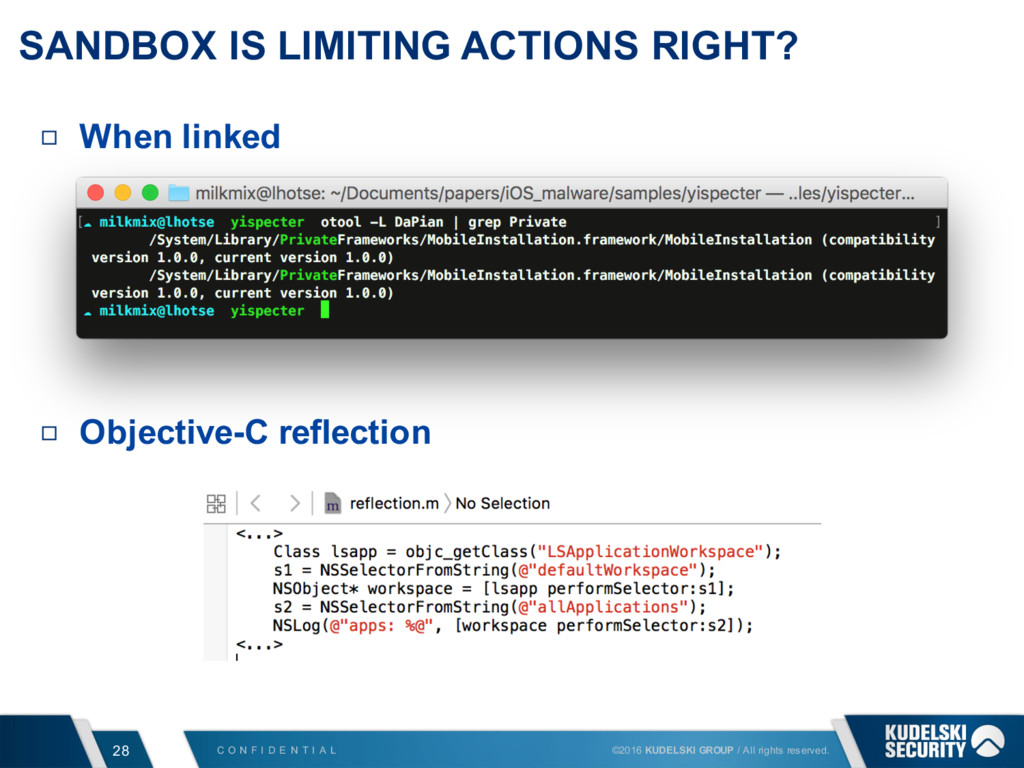
A L 26 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? Listing private APIs functions Nicolas Seriot online list Using classdump-dyld on a jailbroken device Calling private APIs Can be called directly Through dynamic loading dlopen / dlsym Using Objective-C reflection property
C O N F I D E N T I
A L 27 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? Listing private APIs functions
C O N F I D E N T I
A L 28 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? When linked Objective-C reflection
C O N F I D E N T I
A L 29 ©2016 KUDELSKI GROUP / All rights reserved. THE IN HOUSE CASE Entitlements Defined at compilation Not validated by Apple outside of the AppStore flow As seen allows to use more sensitive Private API functions Offers more possibilities CoreTelephony framework Notifications on calls or messages IMSI / IMEI retrieval Install applications Access private information …
NON-APPLICATION BASED ATTACKS
C O N F I D E N T I
A L 31 ©2016 KUDELSKI GROUP / All rights reserved. CONFIGURATION PROFILES Probably used in your organization Configure email client Device certificate Corporate WiFi credentials … Also used by attackers Define proxy and install CA for SSL interception Required to run Enterprise Developer signed applications
PROTECTION AND DETECTION
C O N F I D E N T I
A L 33 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION Mobile devices are more complex to protect Network side Not always using your egress point Web filtering / network monitoring not applicable Endpoint side Operating system less open to 3rd party drivers Applications isolation Not an AV friendly environment
C O N F I D E N T I
A L 34 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE NETWORK IDS like features Use rulesets specific to mobile malware Examples Emerging Threats MOBILE_MALWARE rules Lookout Mobile Threat Intelligence feed Android only AFAIK Detect access to non-corporate configuration Detect download of IPA files signed with external Enterprise Developer accounts
C O N F I D E N T I
A L 35 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Leverage existing MDM/MAM solution Retrieve installed provisioning profiles All external ones should be suspicious Retrieve installed applications bundle names Match known malicious
C O N F I D E N T I
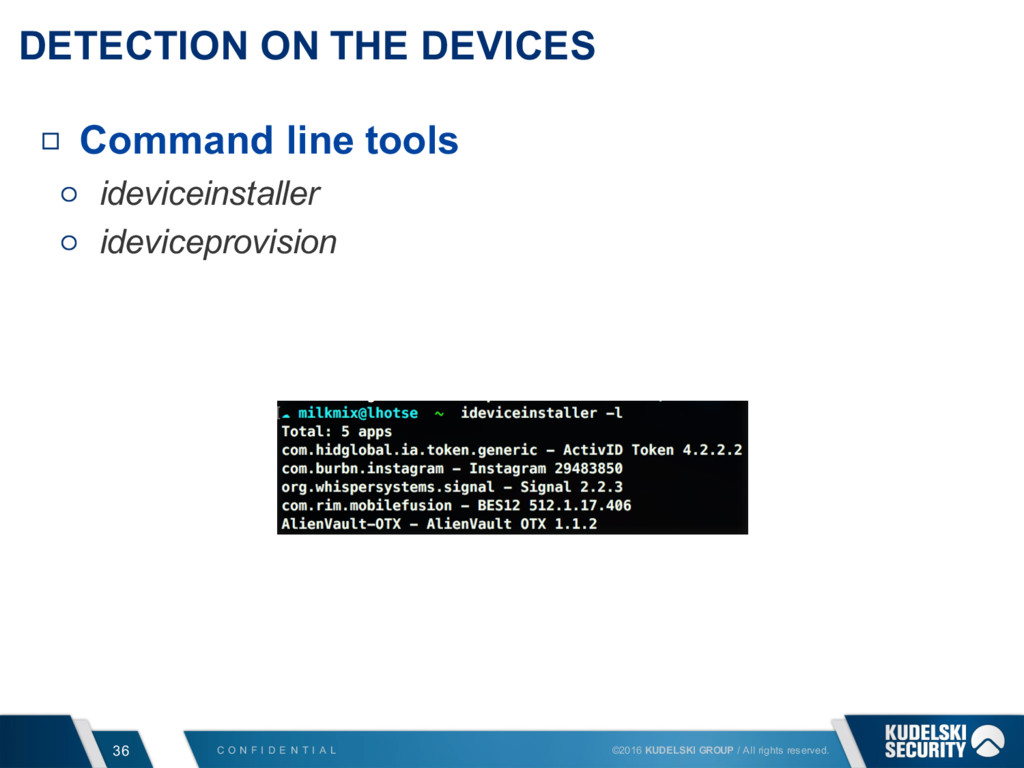
A L 36 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Command line tools ideviceinstaller ideviceprovision
C O N F I D E N T I
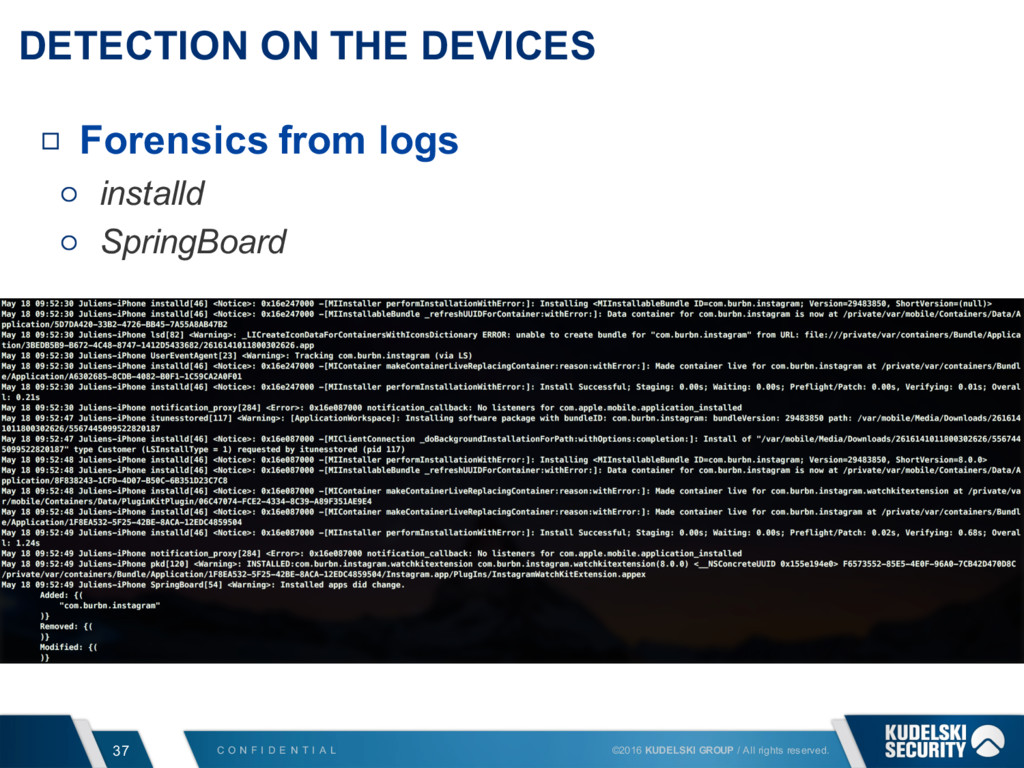
A L 37 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Forensics from logs installd SpringBoard
C O N F I D E N T I
A L 38 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Forensics from side channels logs Battery usage Data usage Both contain applications name and last executed timestamp Available from backups
C O N F I D E N T I
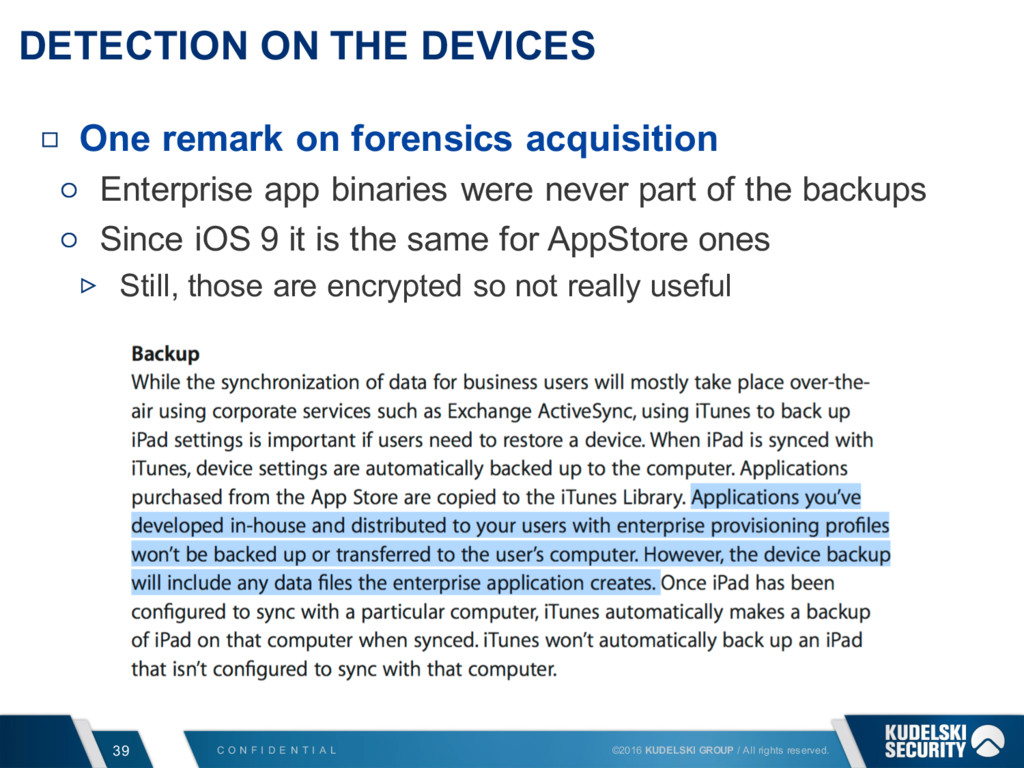
A L 39 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES One remark on forensics acquisition Enterprise app binaries were never part of the backups Since iOS 9 it is the same for AppStore ones Still, those are encrypted so not really useful
C O N F I D E N T I
A L 40 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Future? USB scanning terminal to match known malicious bundles Workstation AV scanning connected devices
C O N F I D E N T I
A L 41 ©2016 KUDELSKI GROUP / All rights reserved. PROTECTION Update devices Decrease potential vulnerabilities exploitation Prevent known jailbreaking methods Device hardening iOS security best-practices Disable AirDrop Force 6-digits passcode …
C O N F I D E N T I
A L 42 ©2016 KUDELSKI GROUP / All rights reserved. PROTECTION Users training Do not install 3rd party provisioning profiles Do not install applications outside of the AppStore or provided by corporate MDM
C O N F I D E N T I
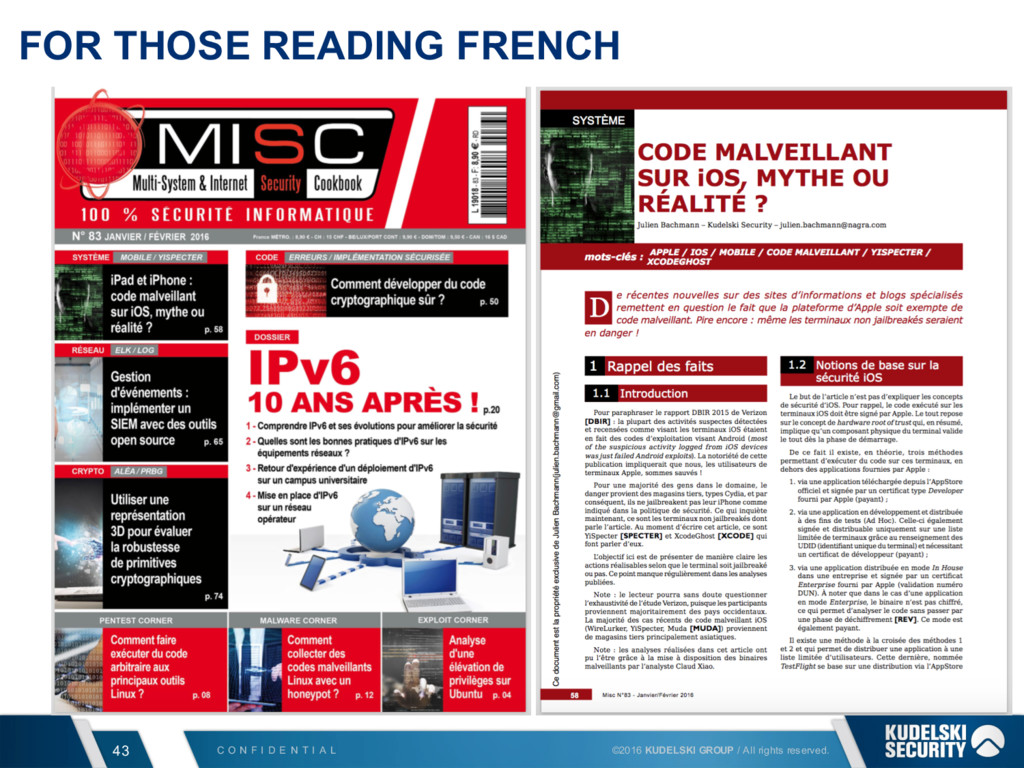
A L 43 ©2016 KUDELSKI GROUP / All rights reserved. FOR THOSE READING FRENCH
C O N F I D E N T I
A L 44 ©2016 KUDELSKI GROUP / All rights reserved. ACKNOWLEDGEMENTS Claud Xiao from Palo Alto for sharing his samples with the research community
C O N F I D E N T I
A L 45 ©2016 KUDELSKI GROUP / All rights reserved.

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 milkmix
 hikaruri
 tatetate55
 10xinc
 magicpod
 nenonaninu
 safie
 ymotongpoo
 cielo1985
 kotaminato
 shimastripe
 nek0128
 i35_267
 eitanlees
 aki_iinuma
 csswizardry
 ianozsvald
 akademiya2063
 gurzu
 trallard
 jacobian
 aleyda
 gr2m
 mfonobong
 panda_program