Share
Embed
Security in an Interconnected and Complex World of Software #appsecapac2014
OWASP Japan
March 20, 2014
Transcript
55 slides
-
Security in an Interconnected and Complex World of So6ware
Michael Coates @_mwc [email protected] -
About • Chairman OWASP Board • Shape
Security – Director of Product Security • Mozilla – Director of Security Assurance • 2012 SC Magazine InfluenJal Security Mind -
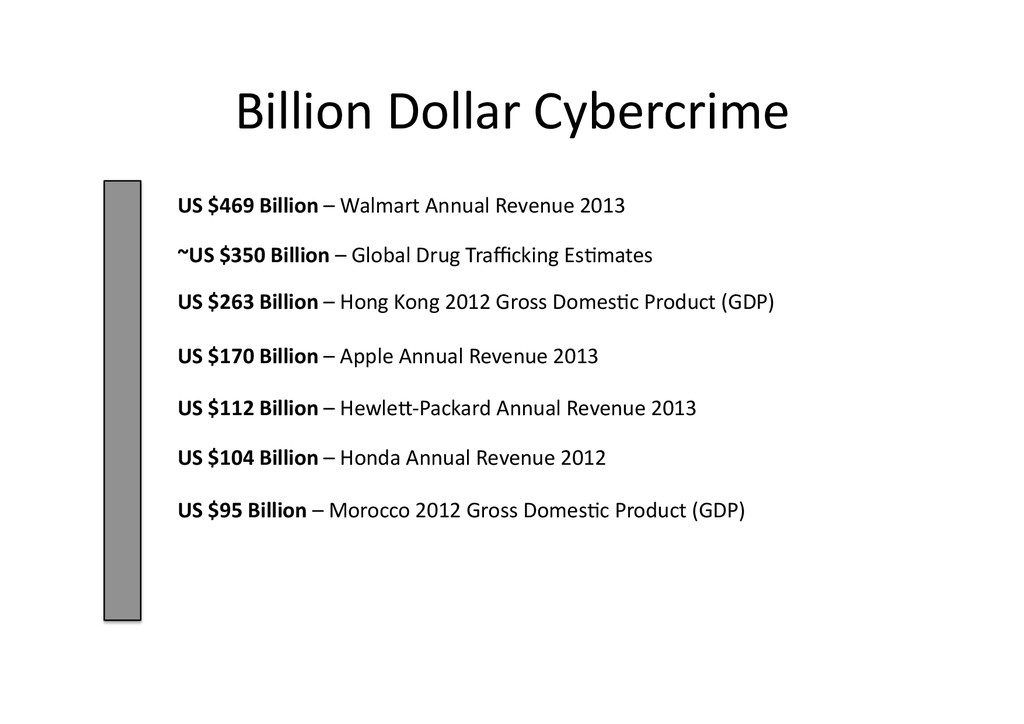
Billion Dollar Cybercrime ~US $350 Billion – Global Drug
Trafficking EsJmates US $170 Billion – Apple Annual Revenue 2013 US $263 Billion – Hong Kong 2012 Gross DomesJc Product (GDP) US $469 Billion – Walmart Annual Revenue 2013 US $95 Billion – Morocco 2012 Gross DomesJc Product (GDP) US $112 Billion – HewleX-‐Packard Annual Revenue 2013 US $104 Billion – Honda Annual Revenue 2012 -
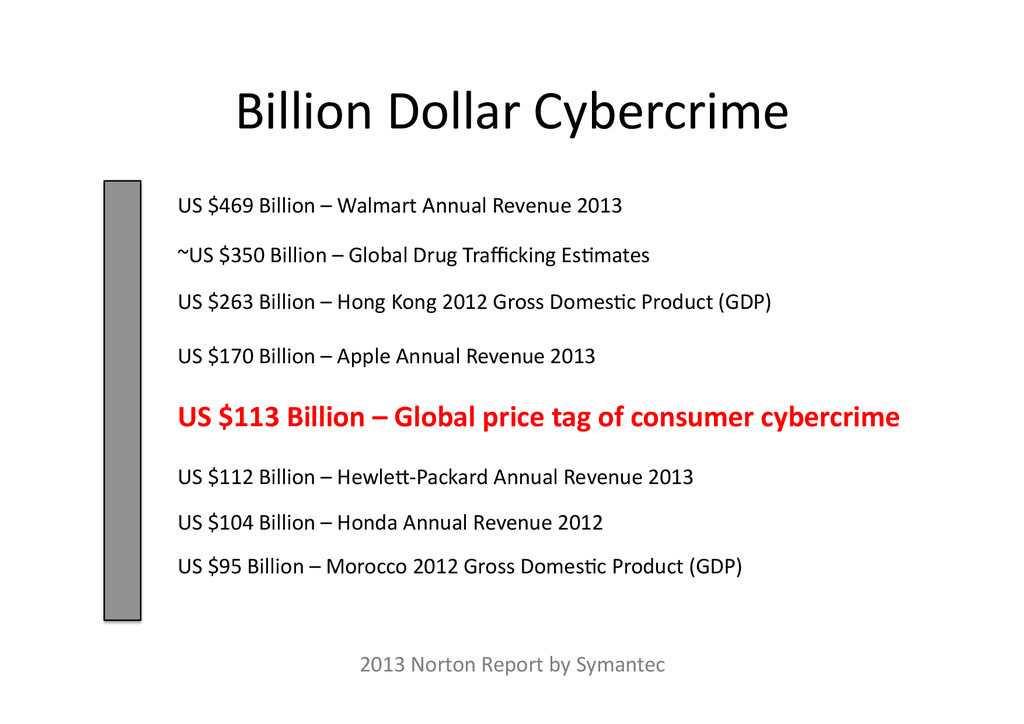
Billion Dollar Cybercrime ~US $350 Billion – Global Drug
Trafficking EsJmates US $113 Billion – Global price tag of consumer cybercrime US $170 Billion – Apple Annual Revenue 2013 US $263 Billion – Hong Kong 2012 Gross DomesJc Product (GDP) US $469 Billion – Walmart Annual Revenue 2013 US $95 Billion – Morocco 2012 Gross DomesJc Product (GDP) US $112 Billion – HewleX-‐Packard Annual Revenue 2013 US $104 Billion – Honda Annual Revenue 2012 2013 Norton Report by Symantec -
Cost of Security • Cybercrime cost to companies
– 26% increase 2012 to 2013 • Cybercrime cost to individual – 50% increase 2012 to 2013 • Cost per breached record to company – Average US $136 / JPY ¥13,923 -
Hacking Becomes Leading Cause of Data Breaches Another
Day, Another Retailer in a Massive Credit Card Breach Secret Service invesJgaJng possible data breach at Sears Report: Verizon Uncovers Two More Retail Breaches … Adobe Breach Impacted At Least 38 Million Users -
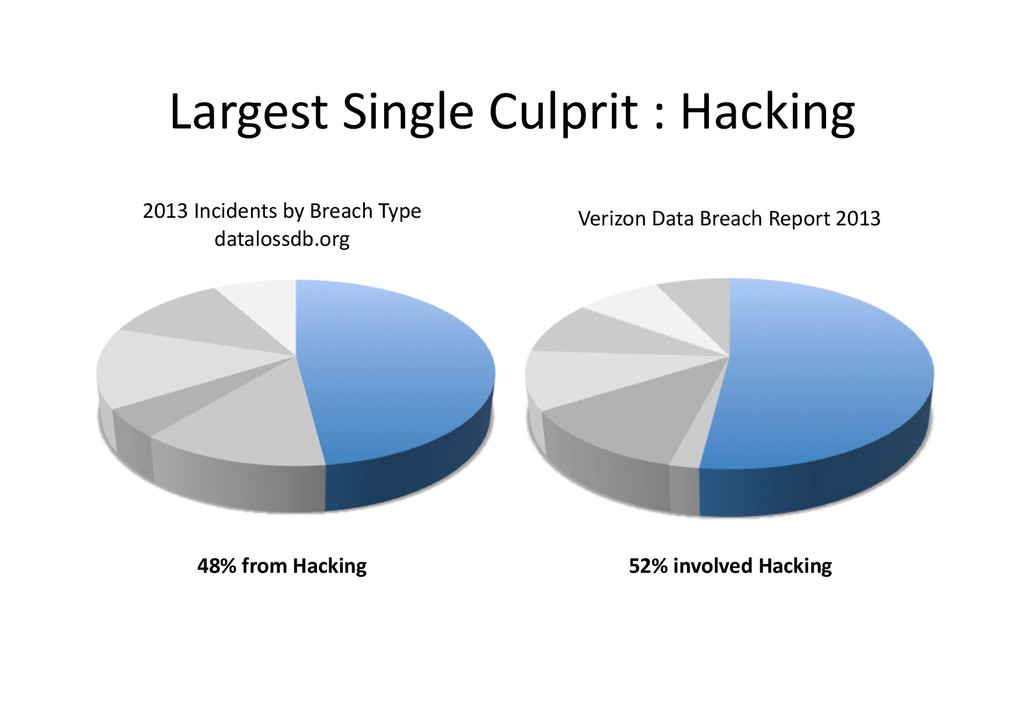
Largest Single Culprit : Hacking Verizon Data Breach Report
2013 2013 Incidents by Breach Type datalossdb.org 48% from Hacking 52% involved Hacking -
Enemy • Script Kiddies – Scanners & generic tools
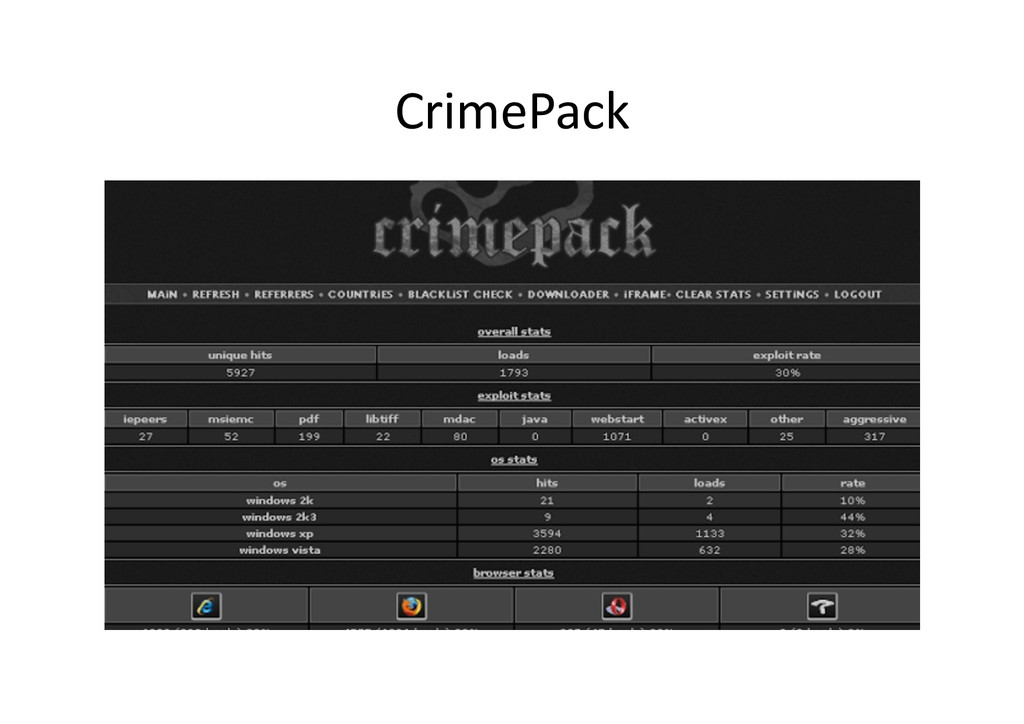
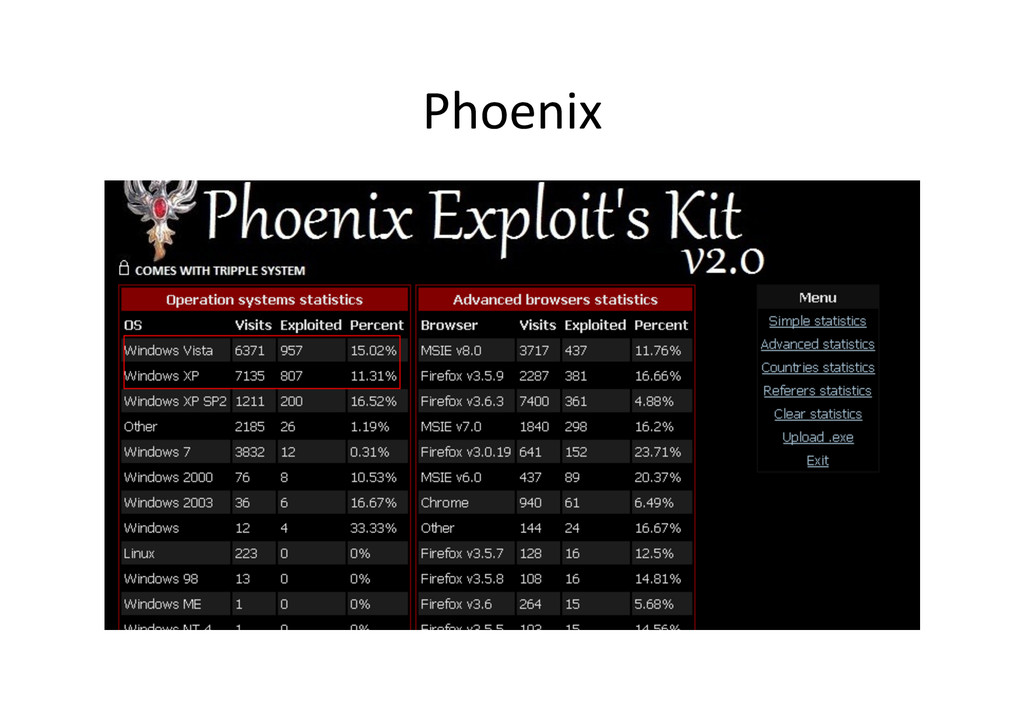
• Organized Crime – Exploit kits • Targeted & Specialized – Precise, 0-‐day, determined -
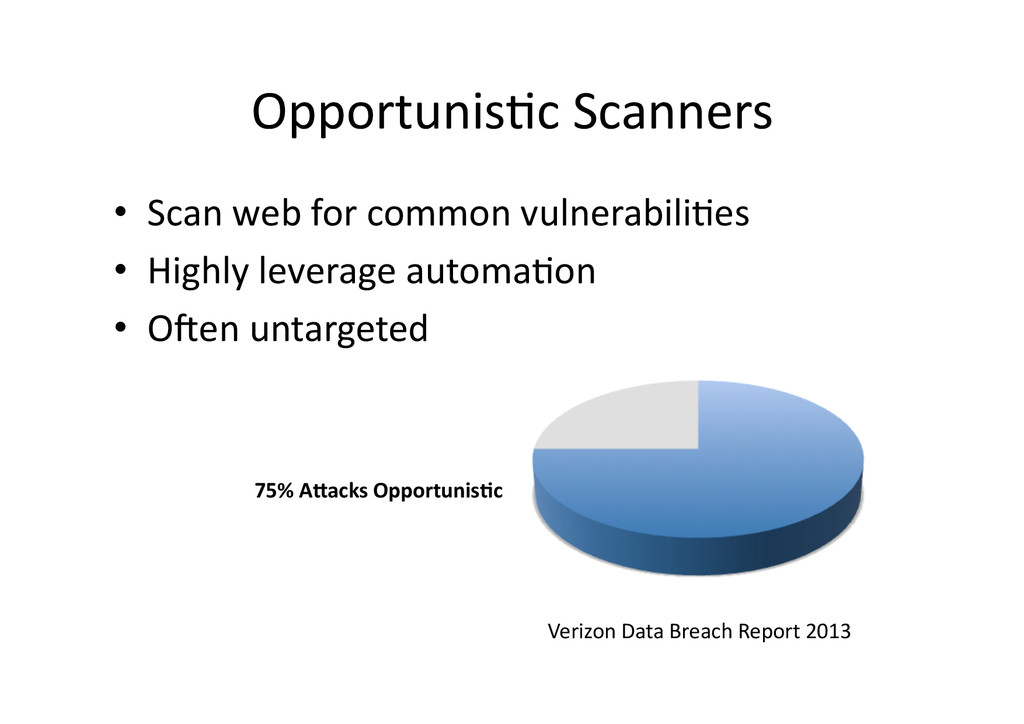
OpportunisJc Scanners • Scan web for common vulnerabiliJes
• Highly leverage automaJon • O6en untargeted 75% AOacks OpportunisQc Verizon Data Breach Report 2013 -
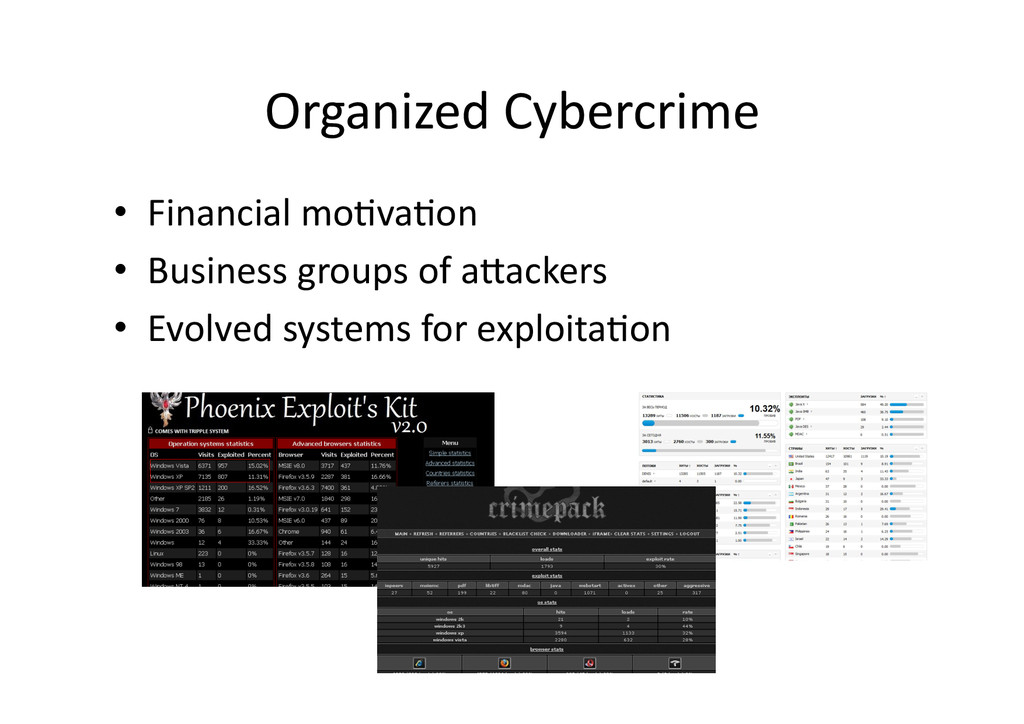
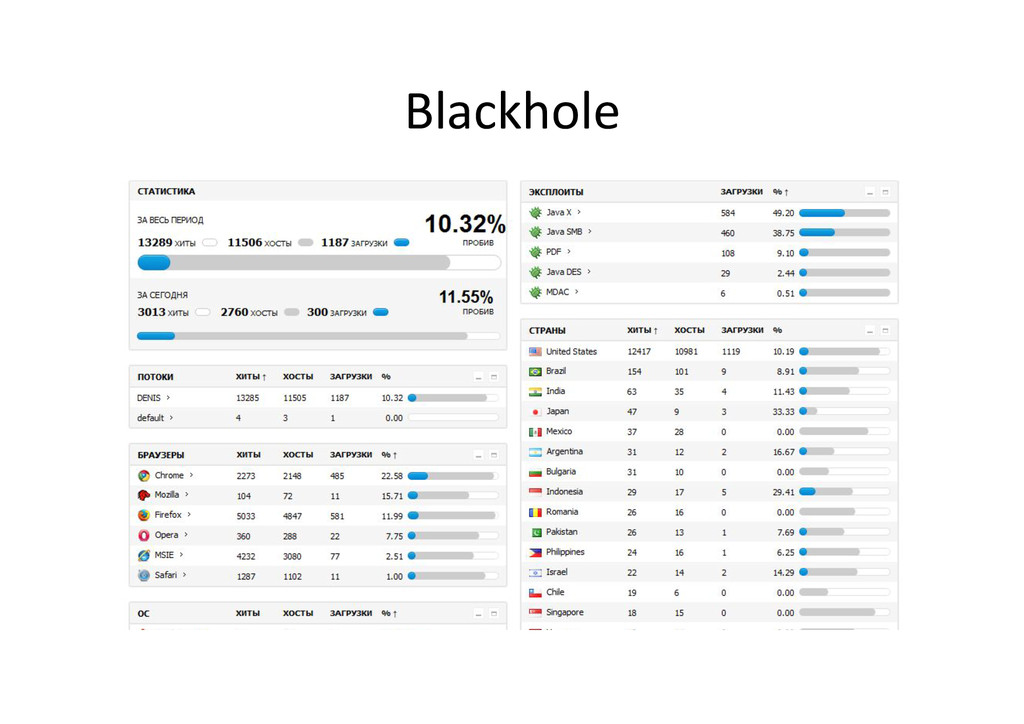
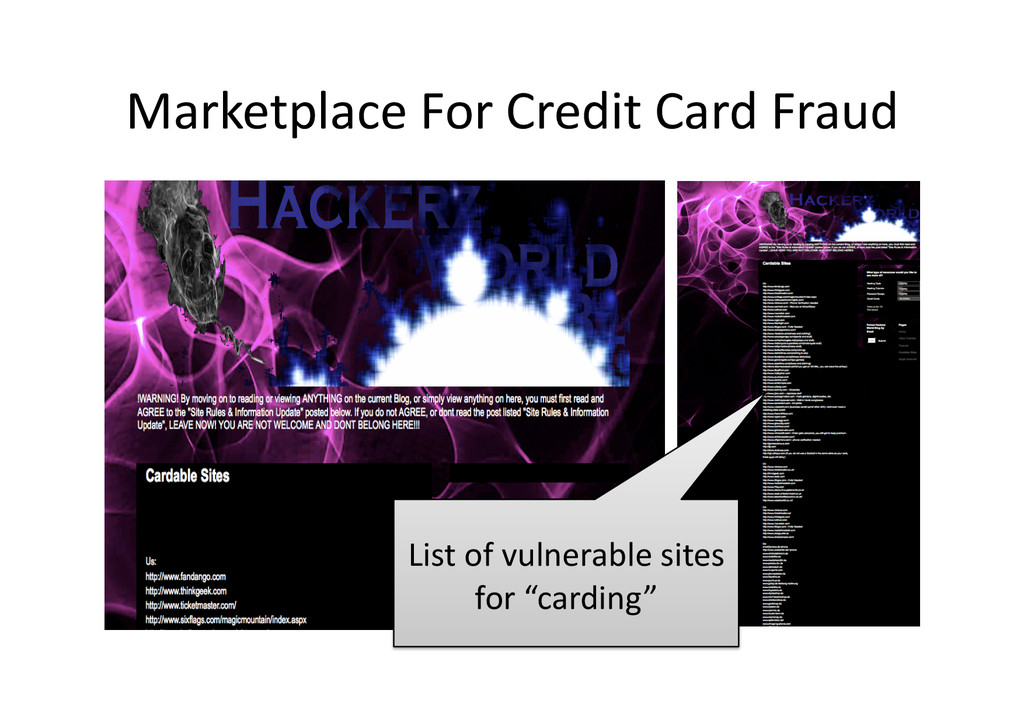
Organized Cybercrime • Financial moJvaJon • Business groups
of aXackers • Evolved systems for exploitaJon -
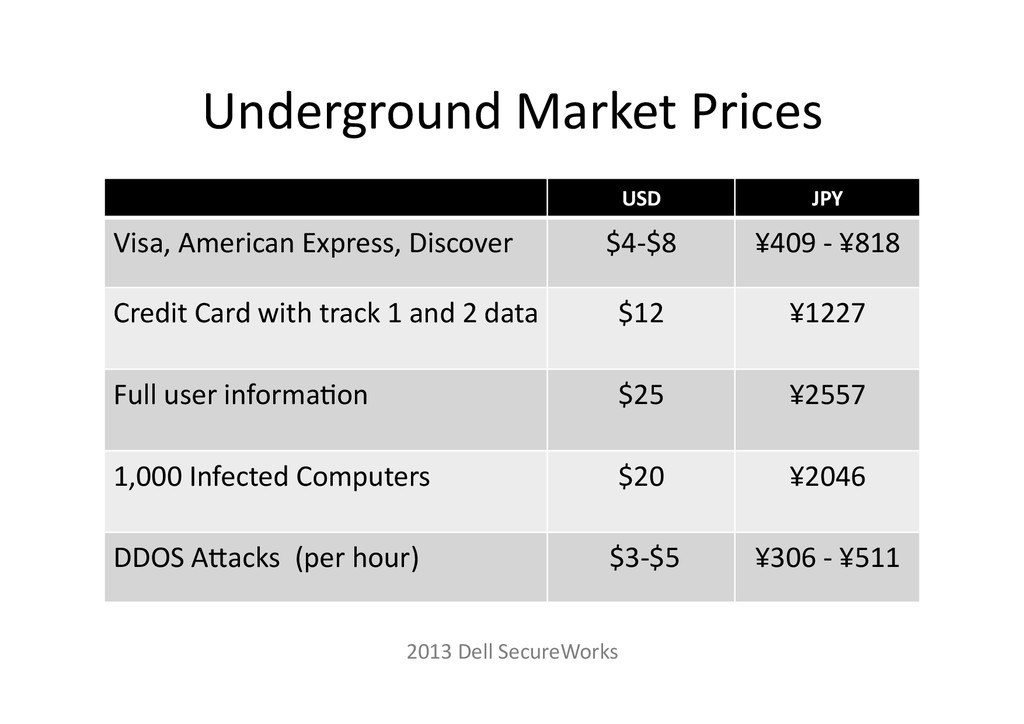
Underground Market Prices 2013 Dell SecureWorks USD
JPY Visa, American Express, Discover $4-‐$8 ¥409 -‐ ¥818 Credit Card with track 1 and 2 data $12 ¥1227 Full user informaJon $25 ¥2557 1,000 Infected Computers $20 ¥2046 DDOS AXacks (per hour) $3-‐$5 ¥306 -‐ ¥511 -
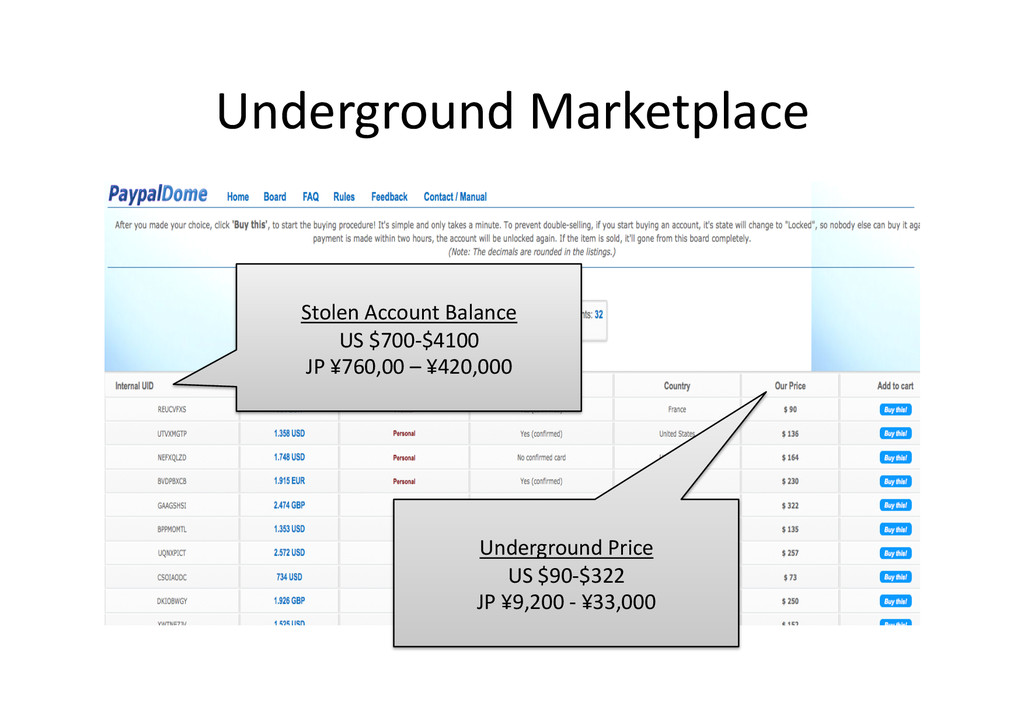
Underground Marketplace Stolen Account Balance US $700-‐$4100
JP ¥760,00 – ¥420,000 Underground Price US $90-‐$322 JP ¥9,200 -‐ ¥33,000 -
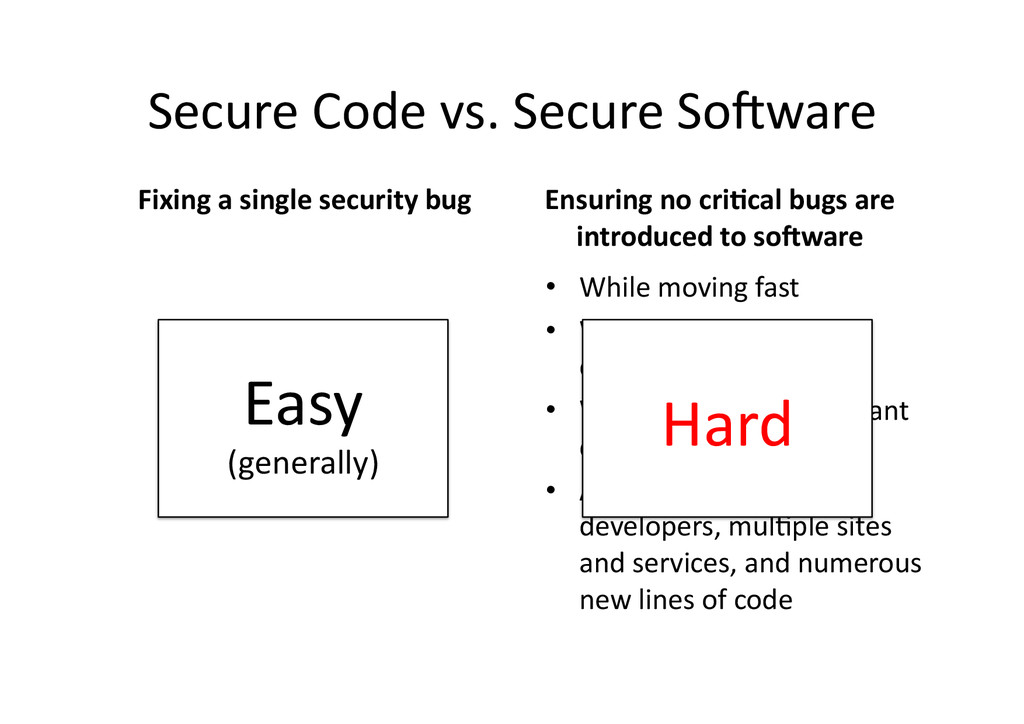
Secure Code vs. Secure So6ware Fixing a single security
bug Ensuring no criQcal bugs are introduced to so]ware -
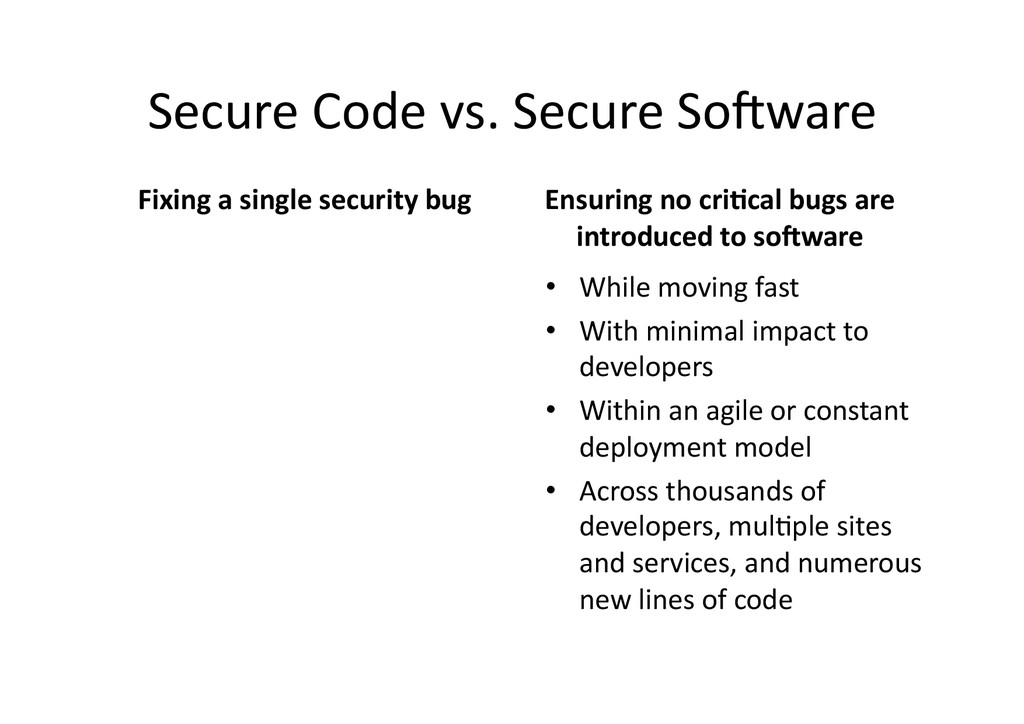
Secure Code vs. Secure So6ware Fixing a single security
bug • While moving fast • With minimal impact to developers • Within an agile or constant deployment model • Across thousands of developers, mulJple sites and services, and numerous new lines of code Ensuring no criQcal bugs are introduced to so]ware -
Secure Code vs. Secure So6ware Fixing a single security
bug • While moving fast • With minimal impact to developers • Within an agile or constant deployment model • Across thousands of developers, mulJple sites and services, and numerous new lines of code Ensuring no criQcal bugs are introduced to so]ware Hard Easy (generally) -
QuesJon the Models • Industry Drivers – PCI, Sarbanes
Oxley, Hipaa, Self RegulaJon • Business Drivers – InnovaJon, fail fast, Jme to market, compeJJve disadvantage • Development PracJces – Code Reuse, Libraries, Patching -
Standards Based Security is Failing • MoJvates for compliance
over security • Complex & unrealisJc in many scenarios • RetroacJve removal of cerJficaJon -
Business MoJvaJon • Security someJmes viewed as tax
• Tradeoff of Jme to market • Put off by aggressive security requirements – An overly secure system used by no one provides no security -
Hiring More Security Isn’t RealisJc Security Professionals – Expensive
– Hard to find – CompeJJon for employment -
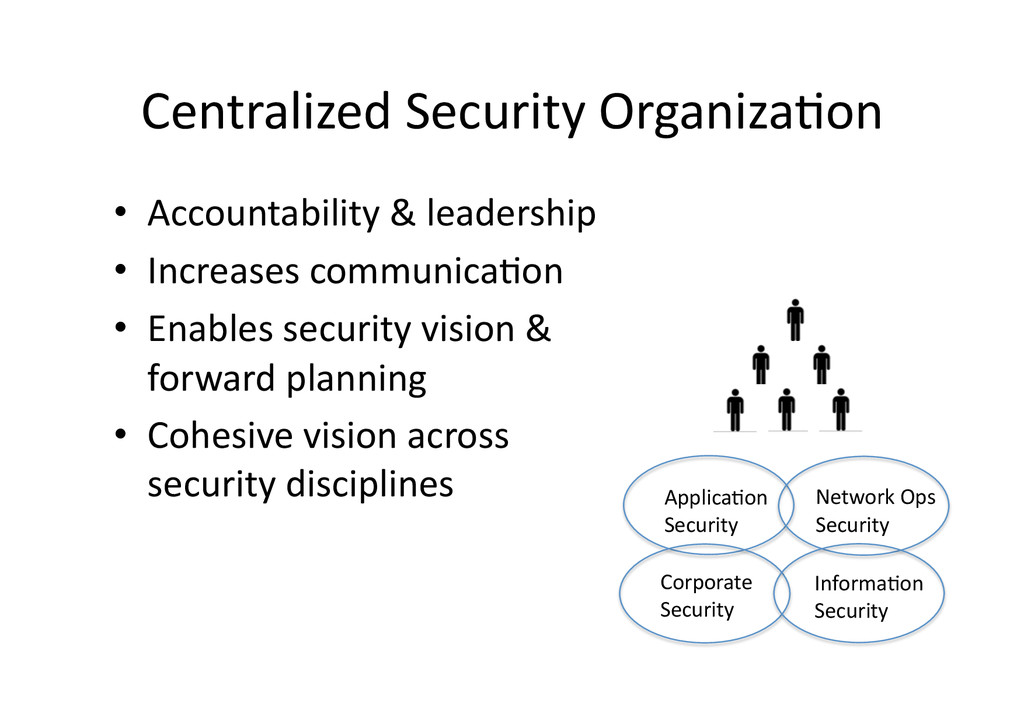
Centralized Security OrganizaJon • Accountability & leadership •
Increases communicaJon • Enables security vision & forward planning • Cohesive vision across security disciplines ApplicaJon Security Network Ops Security Corporate Security InformaJon Security -
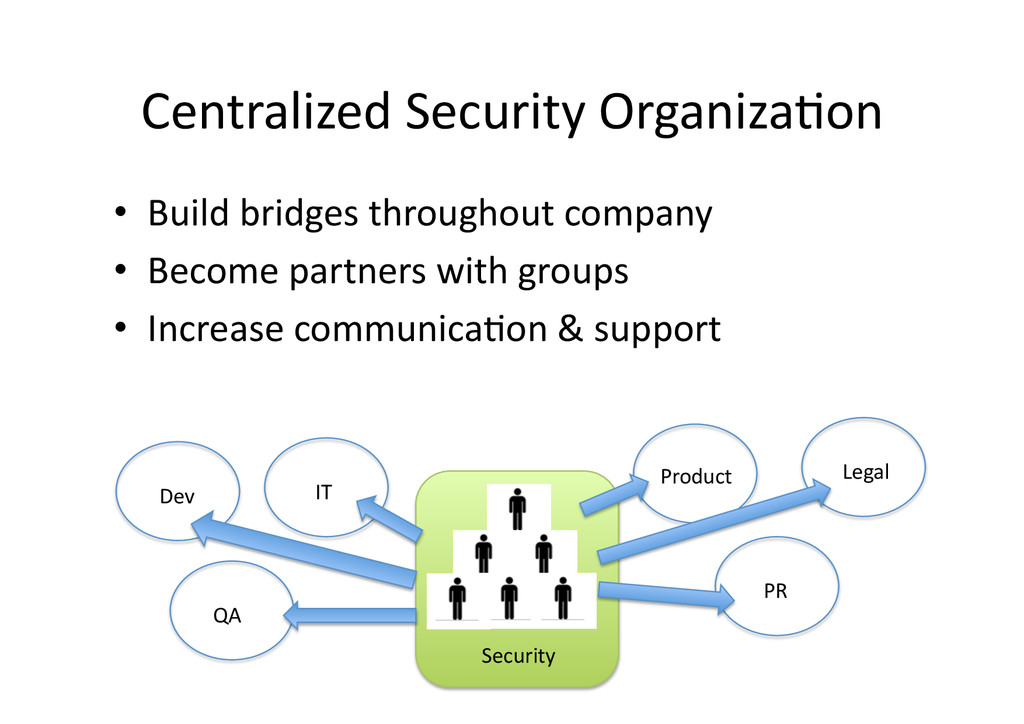
Centralized Security OrganizaJon • Build bridges throughout company
• Become partners with groups • Increase communicaJon & support Dev QA Product PR IT Legal Security -
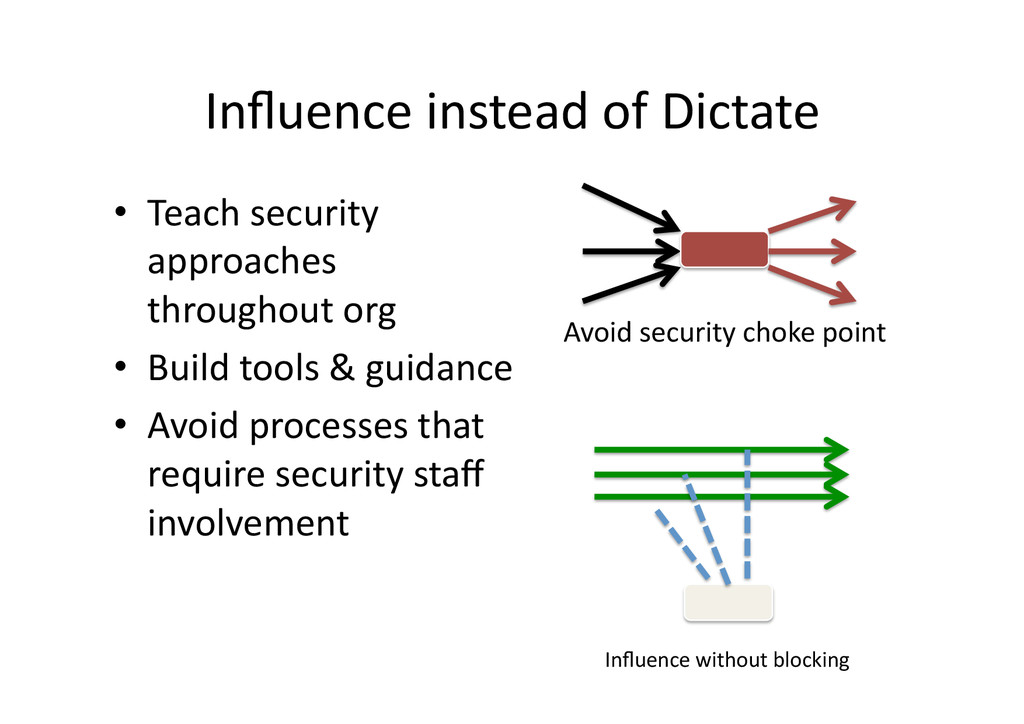
Influence instead of Dictate • Teach security approaches
throughout org • Build tools & guidance • Avoid processes that require security staff involvement Avoid security choke point Influence without blocking -
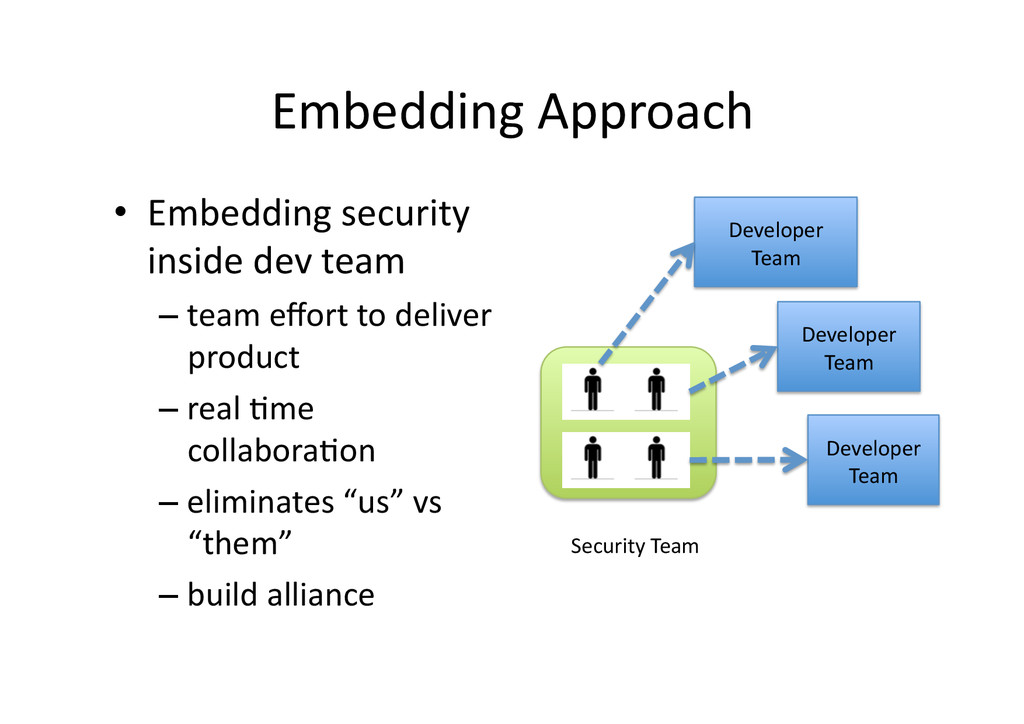
Embedding Approach • Embedding security inside dev team
– team effort to deliver product – real Jme collaboraJon – eliminates “us” vs “them” – build alliance Developer Team Developer Team Developer Team Security Team -
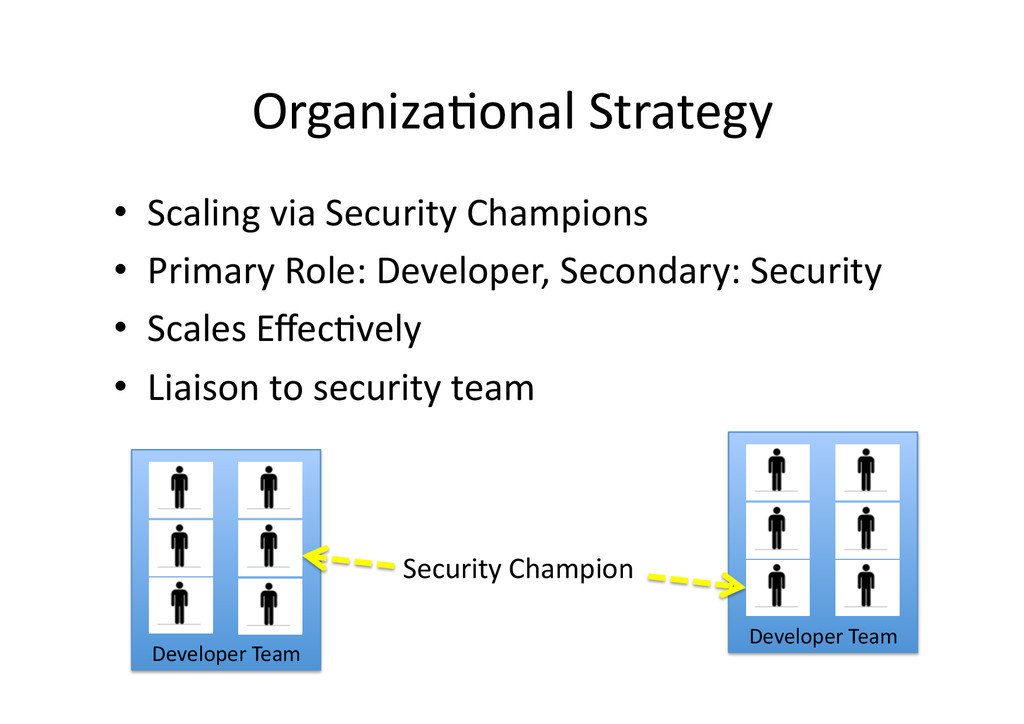
OrganizaJonal Strategy • Scaling via Security Champions •
Primary Role: Developer, Secondary: Security • Scales EffecJvely • Liaison to security team Developer Team Security Champion Developer Team -
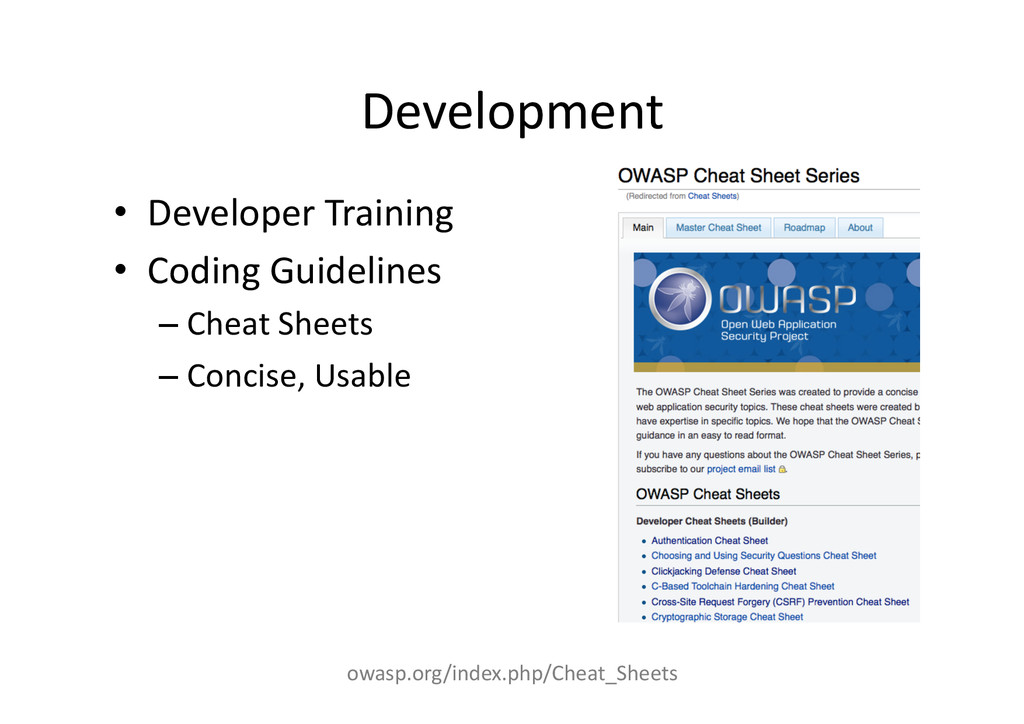
Development • Developer Training • Coding Guidelines
– Cheat Sheets – Concise, Usable owasp.org/index.php/Cheat_Sheets -
Development • Security Libraries & Services – Abstract away
internals of security code – Standardized security libraries • OWASP ESAPI – an example of what you should build within your organizaJon • Engineered web services for security -
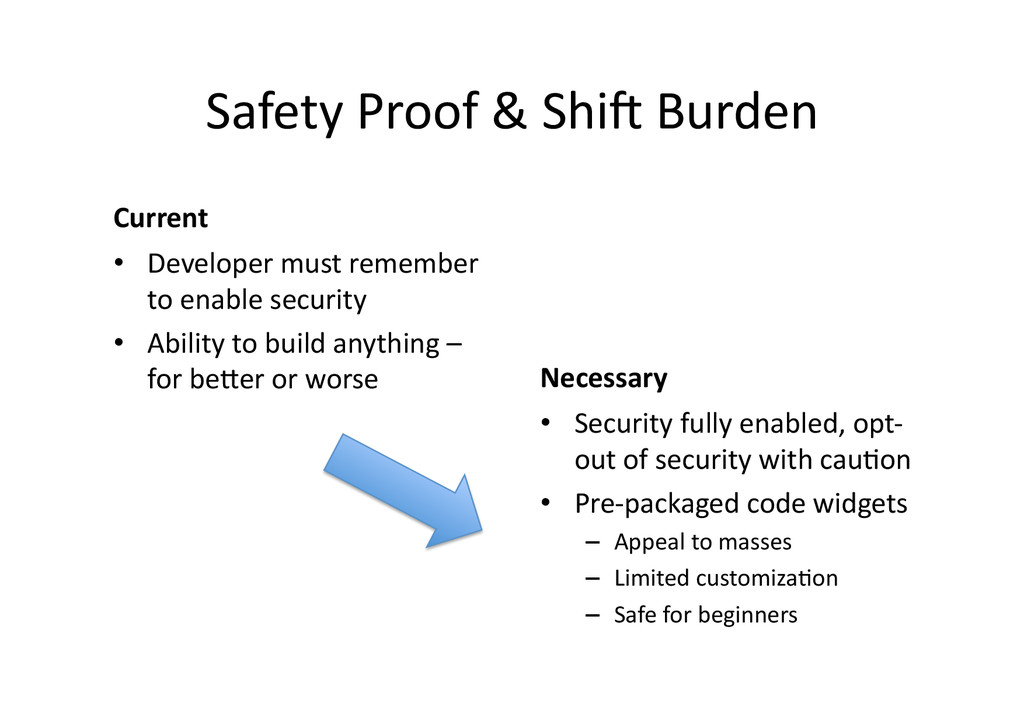
Safety Proof & Shi6 Burden Current • Developer
must remember to enable security • Ability to build anything – for beXer or worse Necessary • Security fully enabled, opt-‐ out of security with cauJon • Pre-‐packaged code widgets – Appeal to masses – Limited customizaJon – Safe for beginners -
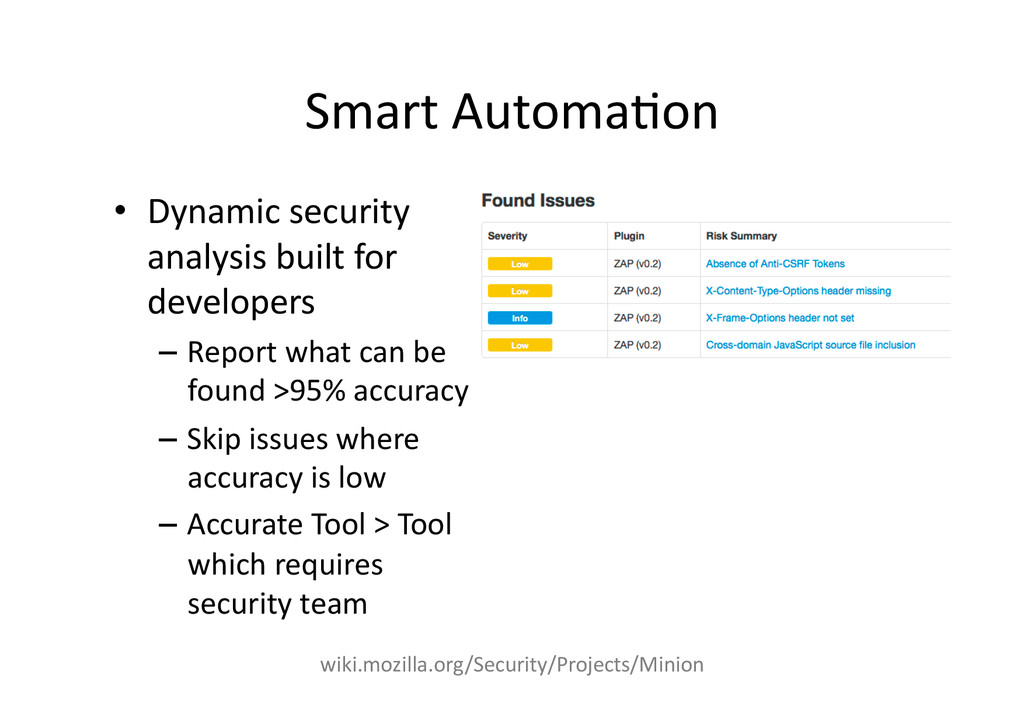
Smart AutomaJon • Dynamic security analysis built for
developers – Report what can be found >95% accuracy – Skip issues where accuracy is low – Accurate Tool > Tool which requires security team wiki.mozilla.org/Security/Projects/Minion -
AutomaJon StaQc / Dynamic Analysis Can scale
if homogenous environment Careful of human involvement Security X as a Service Yes! The Future! -
Quality Assurance • Security validaJon within QA •
FuncJonal tesJng of forms + basic sec tests • Follow paXerns of current QA – Pass / Fail – Self contained tesJng – no need for security evaluaJon “><script>alert(‘problem’)</script> -
Post Release – Defend The App • Detect and
repel common aXacks – Web ApplicaJon Firewall • Detect and repel custom aXacks at business layer – Integrated applicaJon defense – OWASP AppSensor • Disable ability for automated aXacks owasp.org/index.php/OWASP_AppSensor_Project -
Post Release – Defend at Scale • Design for
Scale – Automated aXack blocking & deflecJon – No human analysis in criJcal path. • Human interacJon – Slow – IneffecJve against distributed aXacks -
Key Points Adversary is moJvated and talented – Organized
criminal aXackers – Resourced and focused -
Key Points SaJsfying security standards is a false sense
of security – Focus on acJviJes brining value – Meet required standards & understand lack of value -
Key Points Complex systems require comprehensive security
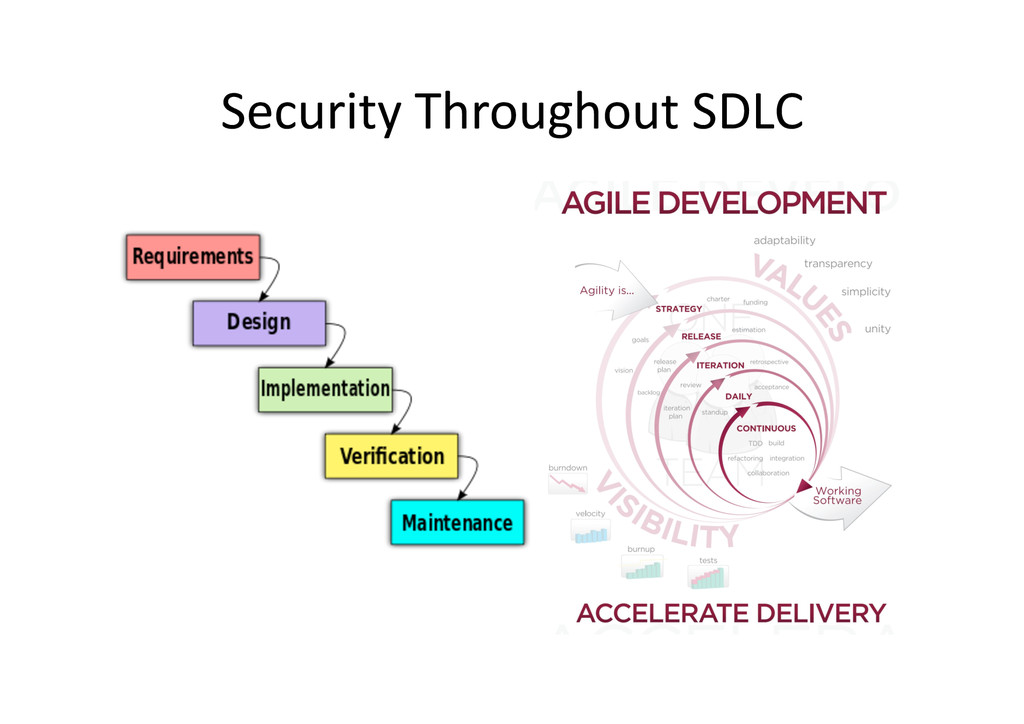
– Integrate security in every step of so6ware development – Build to scale with business needs & development speed