Upgrade to Pro — share decks privately, control downloads, hide ads and more …

AIエージェントの権限管理 1: MCPサーバー・ ツールの Fine grained acc...

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →

AIエージェントの権限管理 1: MCPサーバー・ ツールの Fine grained access control 編

AWS PartnerCast - 1 Day Solution Dive Deep 登壇資料。2026/6/12

AI Agent基盤における、ユーザー毎の MCP サーバー / ツールの権限制御の重要性や、AgentCore を利用したMCPサーバー / ツールの Fine grained access control について解説します。AgentCore Gateway の Inbound Auth / AgentCore Policy / AgentCore Gateway Interceptors の各手法の説明と差分、ユースケースについて整理してます。

Avatar for Renya Kujirada

Renya Kujirada

April 17, 2026

More Decks by Renya Kujirada

Other Decks in Technology

Transcript

  1. UPDATE THIS PRESENTATION HEADER IN SLIDE MASTER AI エージェントの権限管理 1:

    MCP サーバー・ツールの Fine grained access control 編 鯨⽥ 連也 AI/ML Specialist Solutions Architect 2026/06/12 © 2026, Amazon Web © 2026, Services, Amazon Inc. or Web its Services, affiliates.Inc. All or rights its affiliates. reserved.All Amazon rights reserved. Confidential Amazon and Trademark. Confidential and Trademark.
  2. ⾃⼰紹介 鯨⽥ 連也 アマゾン ウェブ サービス ジャパン合同会社 スペシャリスト ソリューションアーキテクト, AI/ML

    前職 (NTT DATA) では、データサイエンティストとして、 深層学習モデル (Computer Vision)・AI Agent の開発に従事。 • 興味: AI Agent 開発, LLM 学習・推論 X: @recat_125 • 好きなサービス: Amazon Bedrock, Amazon SageMaker AI © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 2
  3. 発表の背景と⽬的 今後、企業毎に数百・数千の Agent がデプロイされ、Agent が社内の多数のデータソースや API と 接続するようなことが多くなると考えられる。 セキュアに Agent

    にツールやデータを利⽤させるには Fine-grained access control (FGAC) が重要で ある。AgentCore を利⽤することで、FGAC を容易に実装できる。 本発表では、AgentCore を利⽤した MCP サーバー・ツールの 3種の FGAC の実装パターンについて、 Dive Deep する。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 3
  4. アジェンダ • Agent 利⽤時の FGAC の重要性 • AgentCore Gateway について

    • AgentCore Gateway における MCP サーバー / ツールのアクセス制御⽅法 • MCP サーバーのアクセス制御 (Gateway Inbound authorization) • ツールのアクセス制御 (Policy) • ツールのアクセス制御 (Gateway Interceptors) • 各⼿法の使い分け・⽐較 • まとめ © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 5
  5. Agent 利⽤時の Fine-grained access control (FGAC) の重要性 © 2026, Amazon

    Web Services, Inc. or its affiliates. All rights reserved. 6
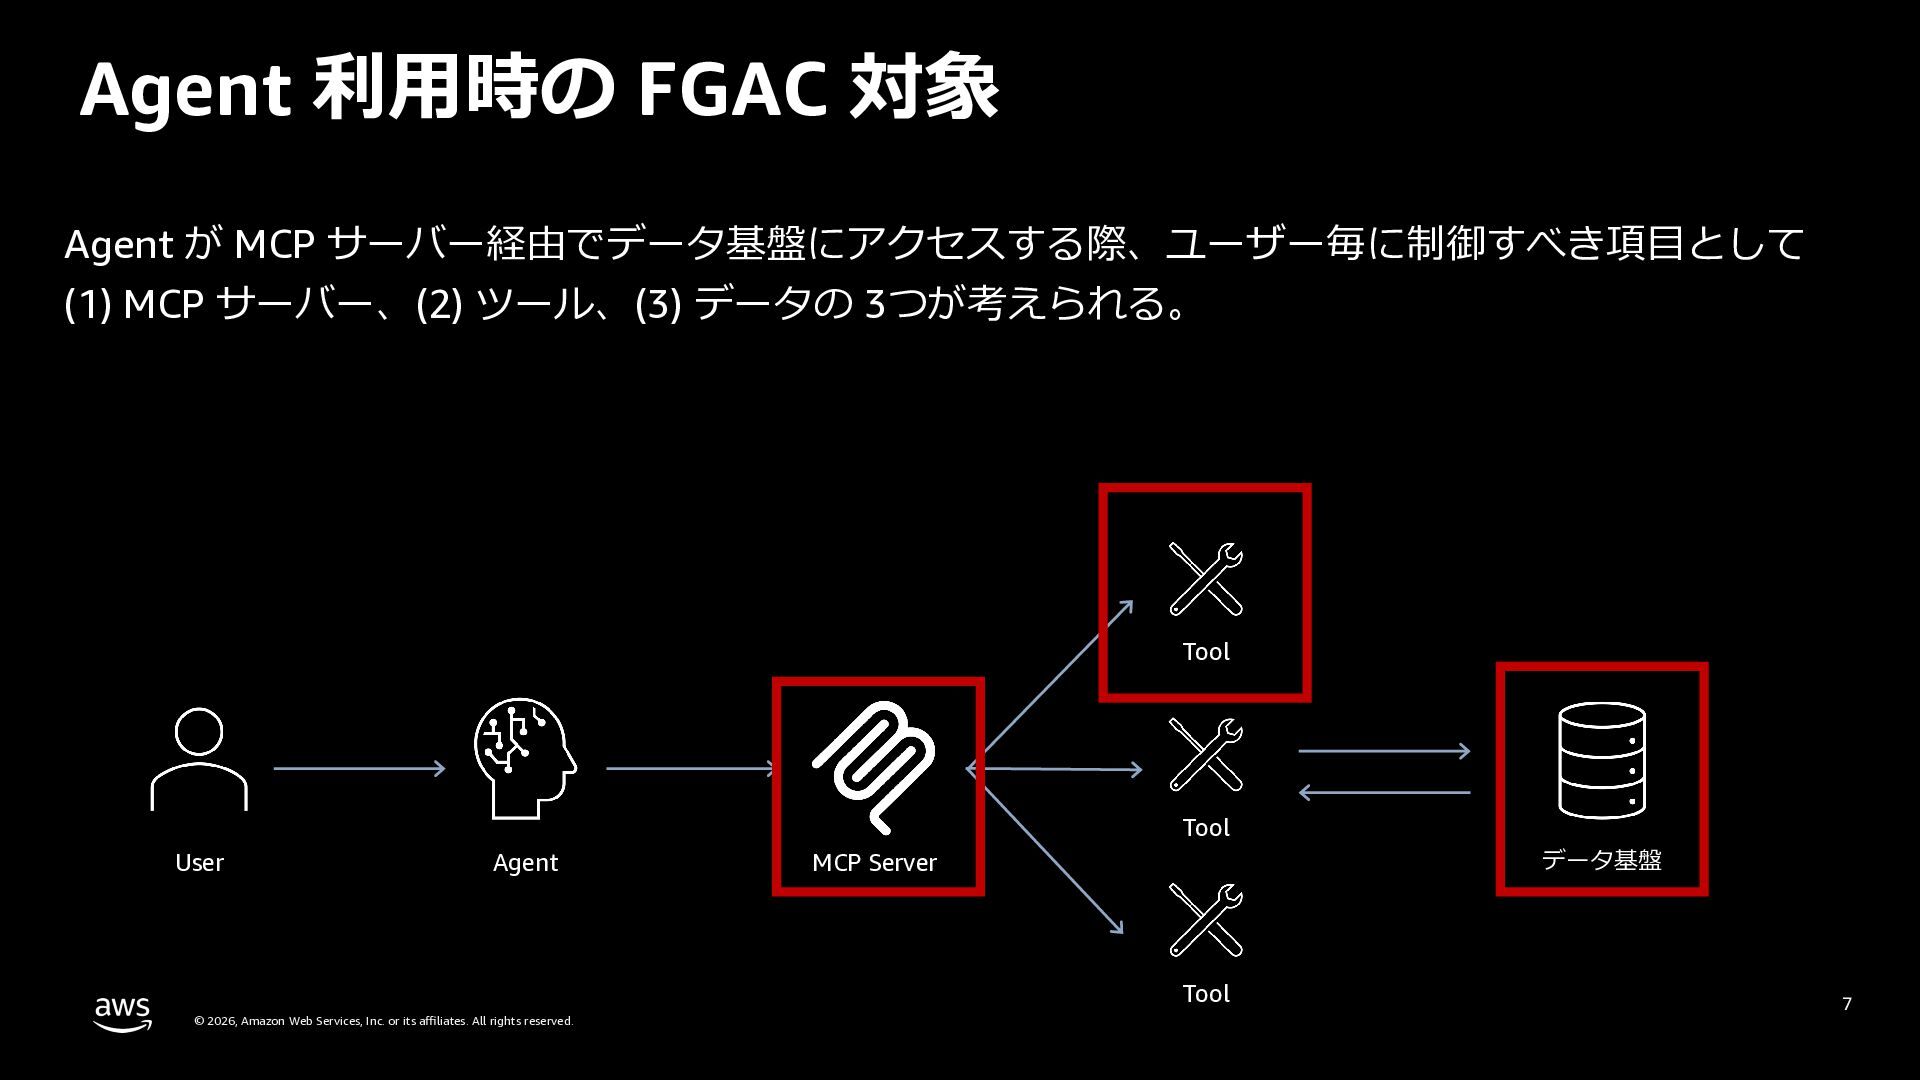
  6. Agent 利⽤時の FGAC 対象 Agent が MCP サーバー経由でデータ基盤にアクセスする際、ユーザー毎に制御すべき項⽬として (1) MCP

    サーバー、(2) ツール、(3) データの 3つが考えられる。 Tool Tool User Agent データ基盤 MCP Server Tool © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 7
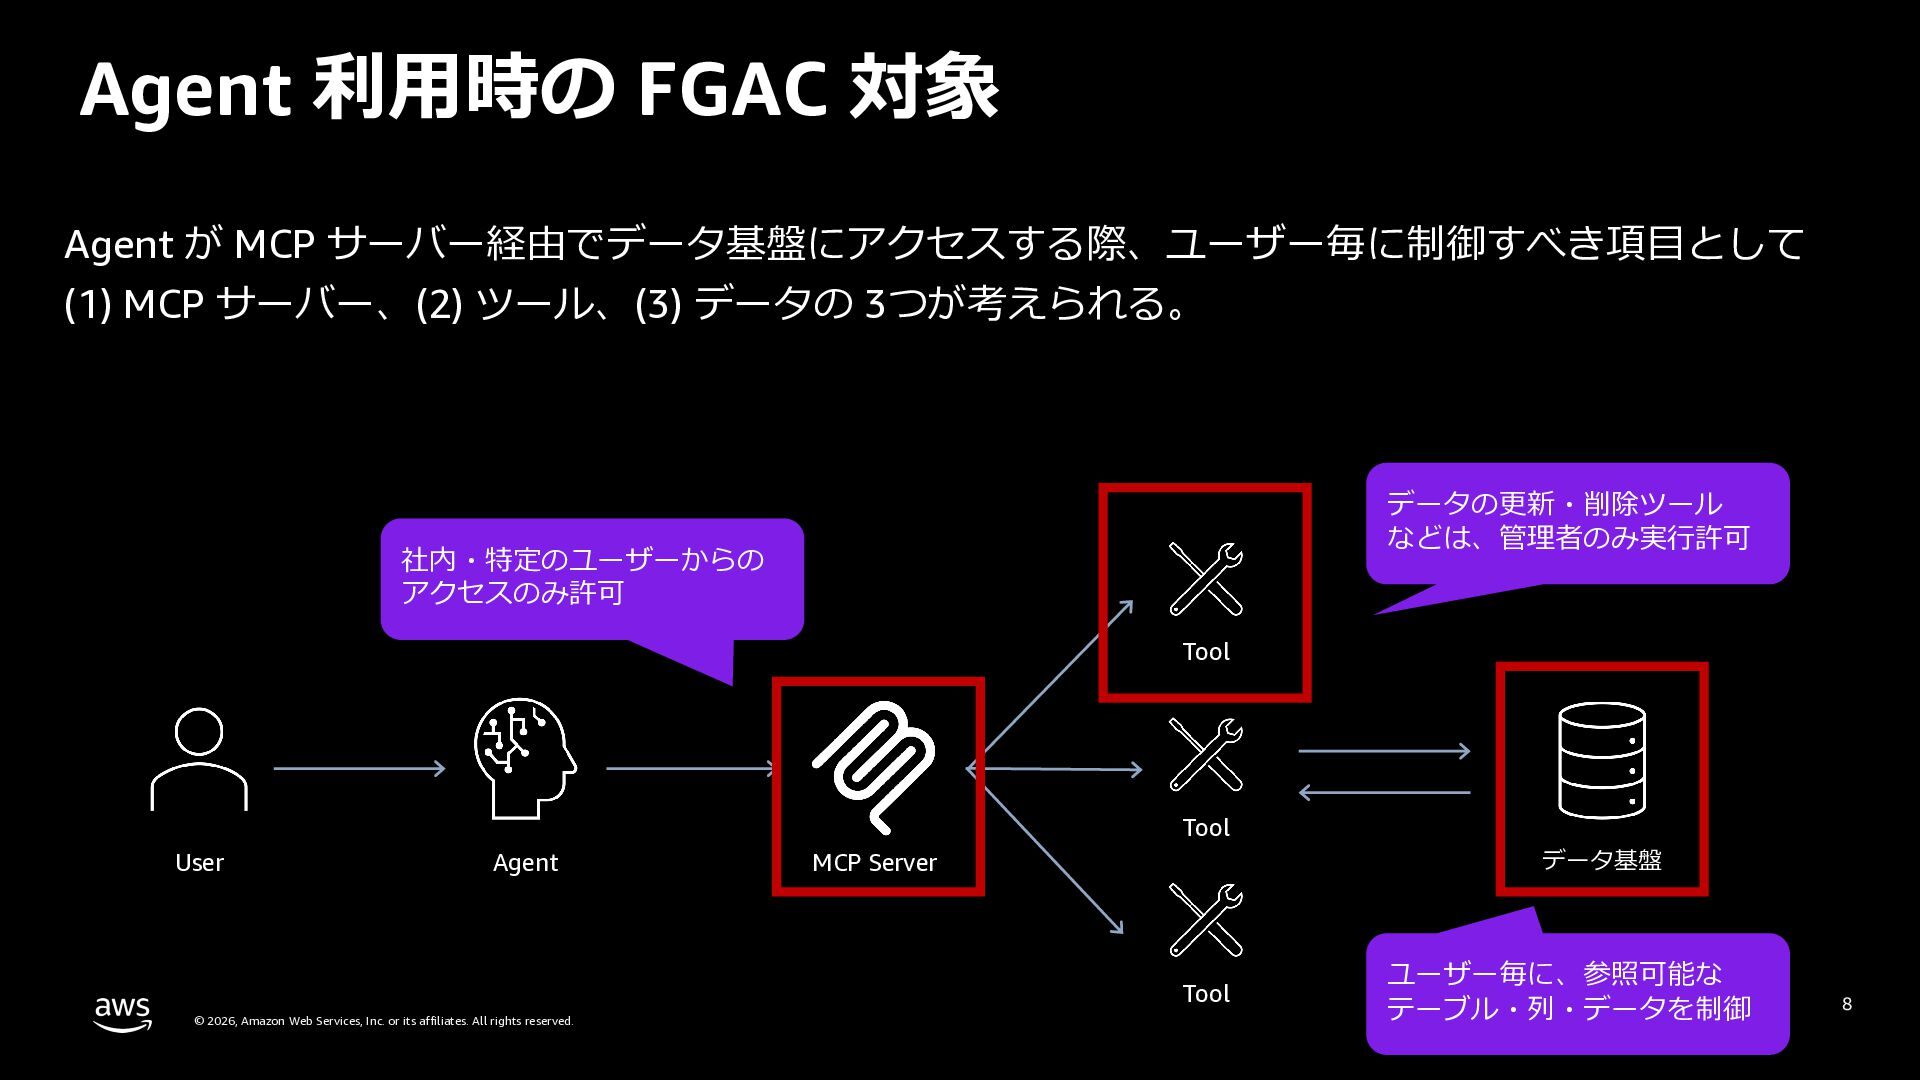
  7. Agent 利⽤時の FGAC 対象 Agent が MCP サーバー経由でデータ基盤にアクセスする際、ユーザー毎に制御すべき項⽬として (1) MCP

    サーバー、(2) ツール、(3) データの 3つが考えられる。 データの更新・削除ツール などは、管理者のみ実⾏許可 社内・特定のユーザーからの アクセスのみ許可 Tool Tool User Agent データ基盤 MCP Server Tool © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ユーザー毎に、参照可能な テーブル・列・データを制御 8
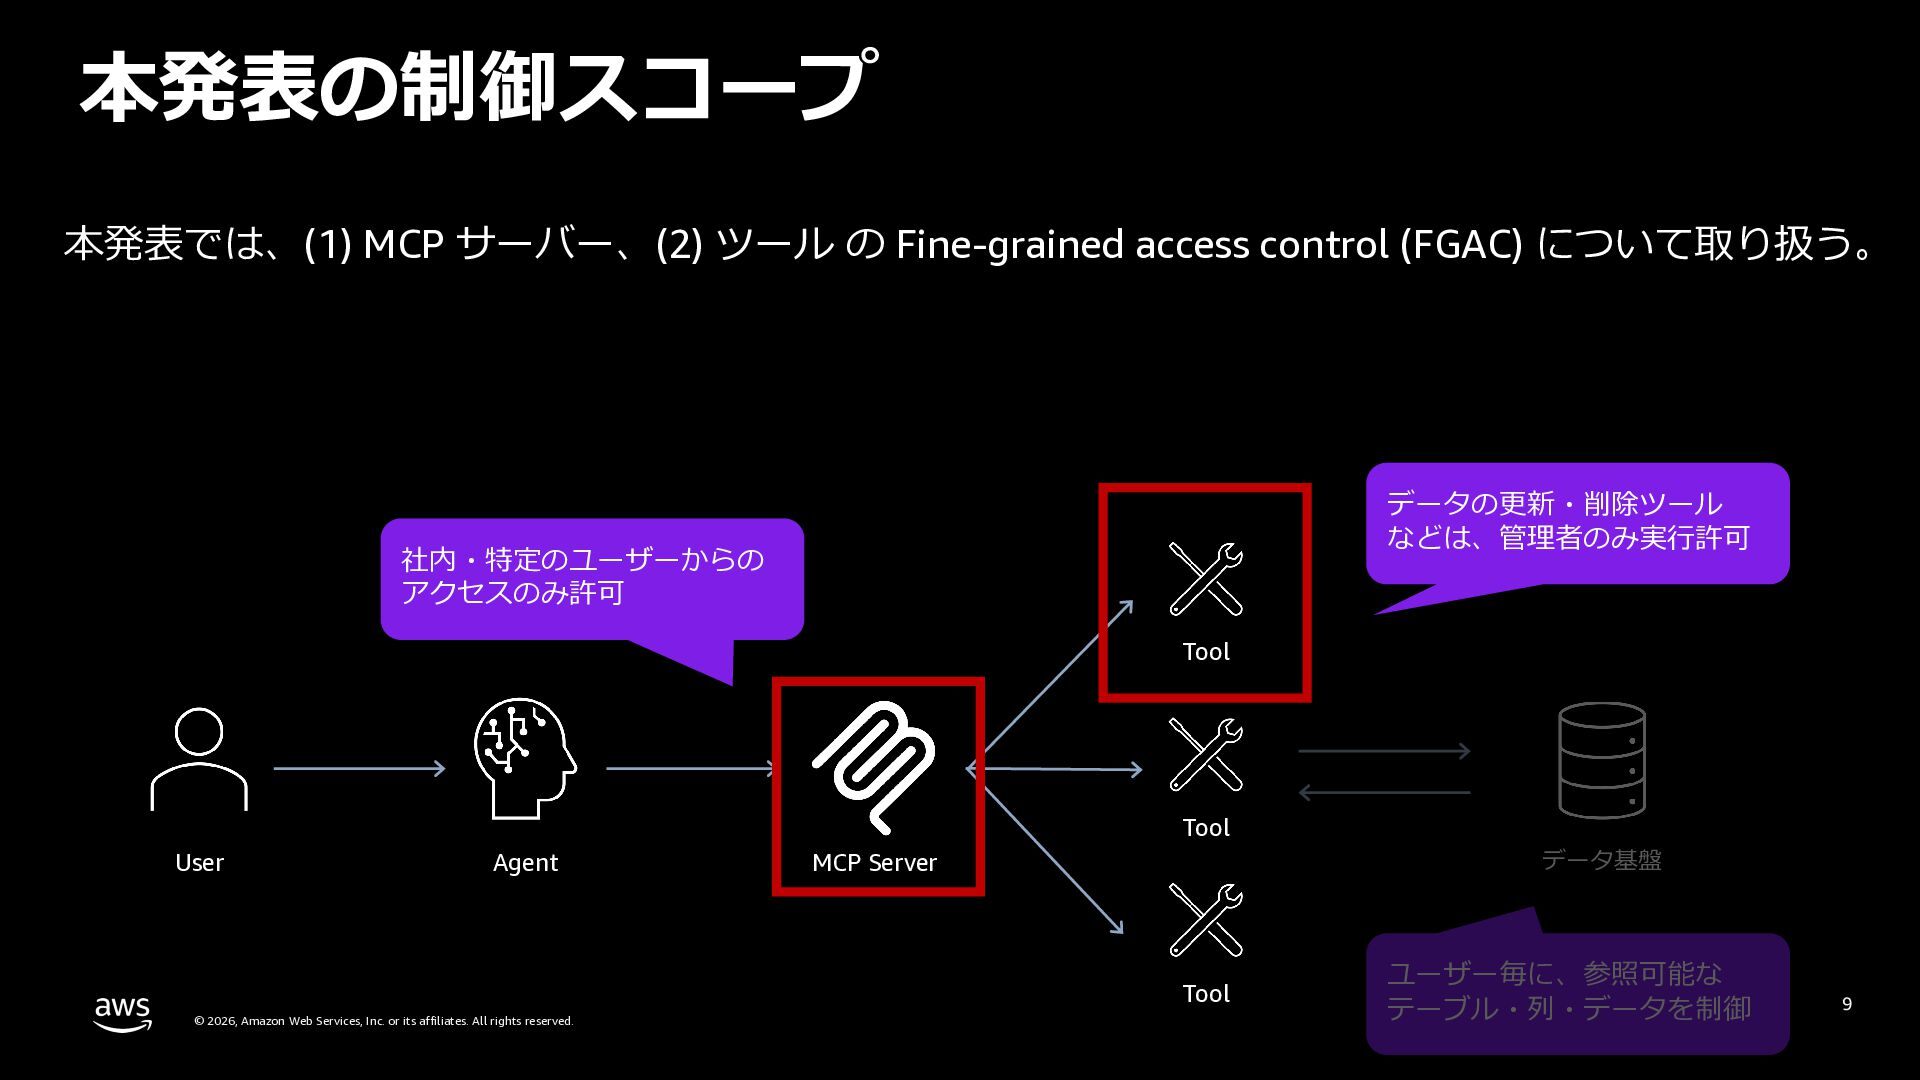
  8. 本発表の制御スコープ 本発表では、(1) MCP サーバー、(2) ツール の Fine-grained access control (FGAC)

    について取り扱う。 データの更新・削除ツール などは、管理者のみ実⾏許可 社内・特定のユーザーからの アクセスのみ許可 Tool Tool User Agent データ基盤 MCP Server Tool © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ユーザー毎に、参照可能な テーブル・列・データを制御 9
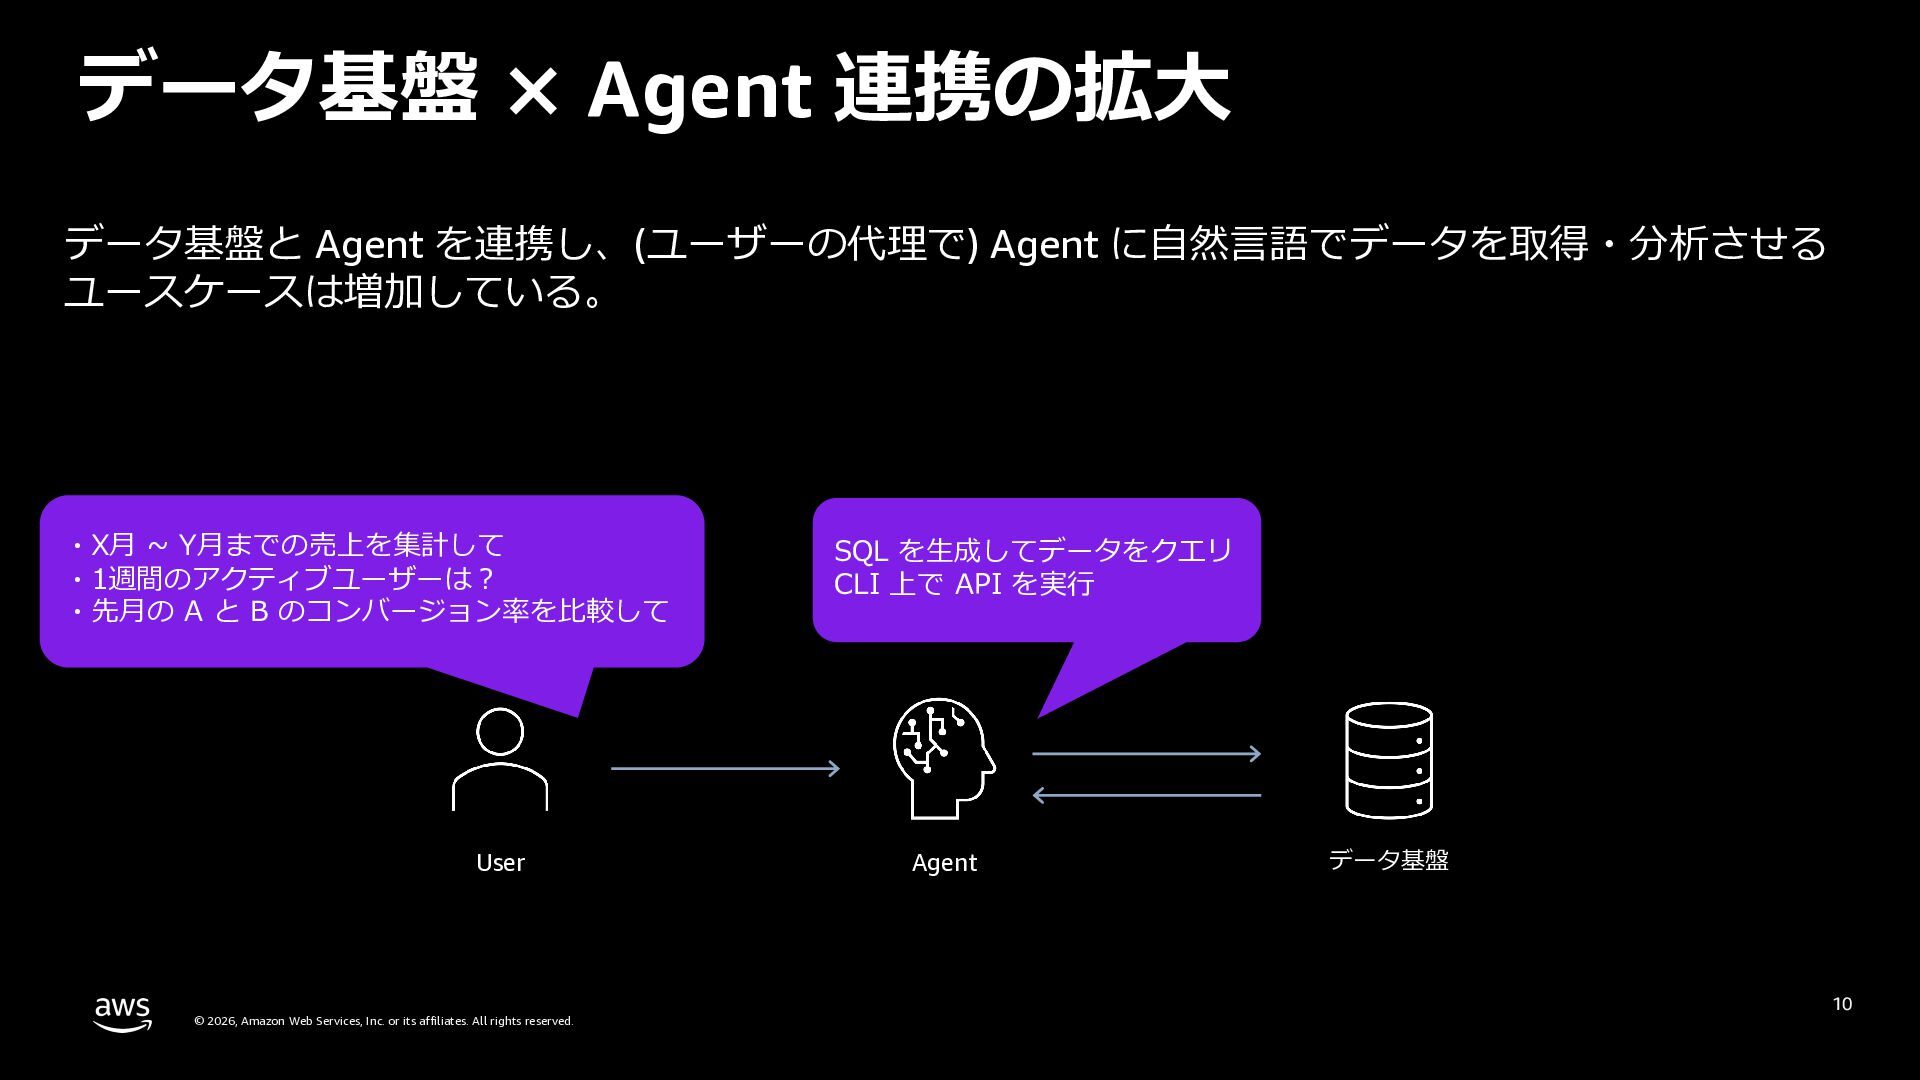
  9. データ基盤 × Agent 連携の拡⼤ データ基盤と Agent を連携し、(ユーザーの代理で) Agent に⾃然⾔語でデータを取得・分析させる ユースケースは増加している。

    ・X⽉ ~ Y⽉までの売上を集計して ・1週間のアクティブユーザーは︖ ・先⽉の A と B のコンバージョン率を⽐較して User © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. SQL を⽣成してデータをクエリ CLI 上で API を実⾏ Agent データ基盤 10
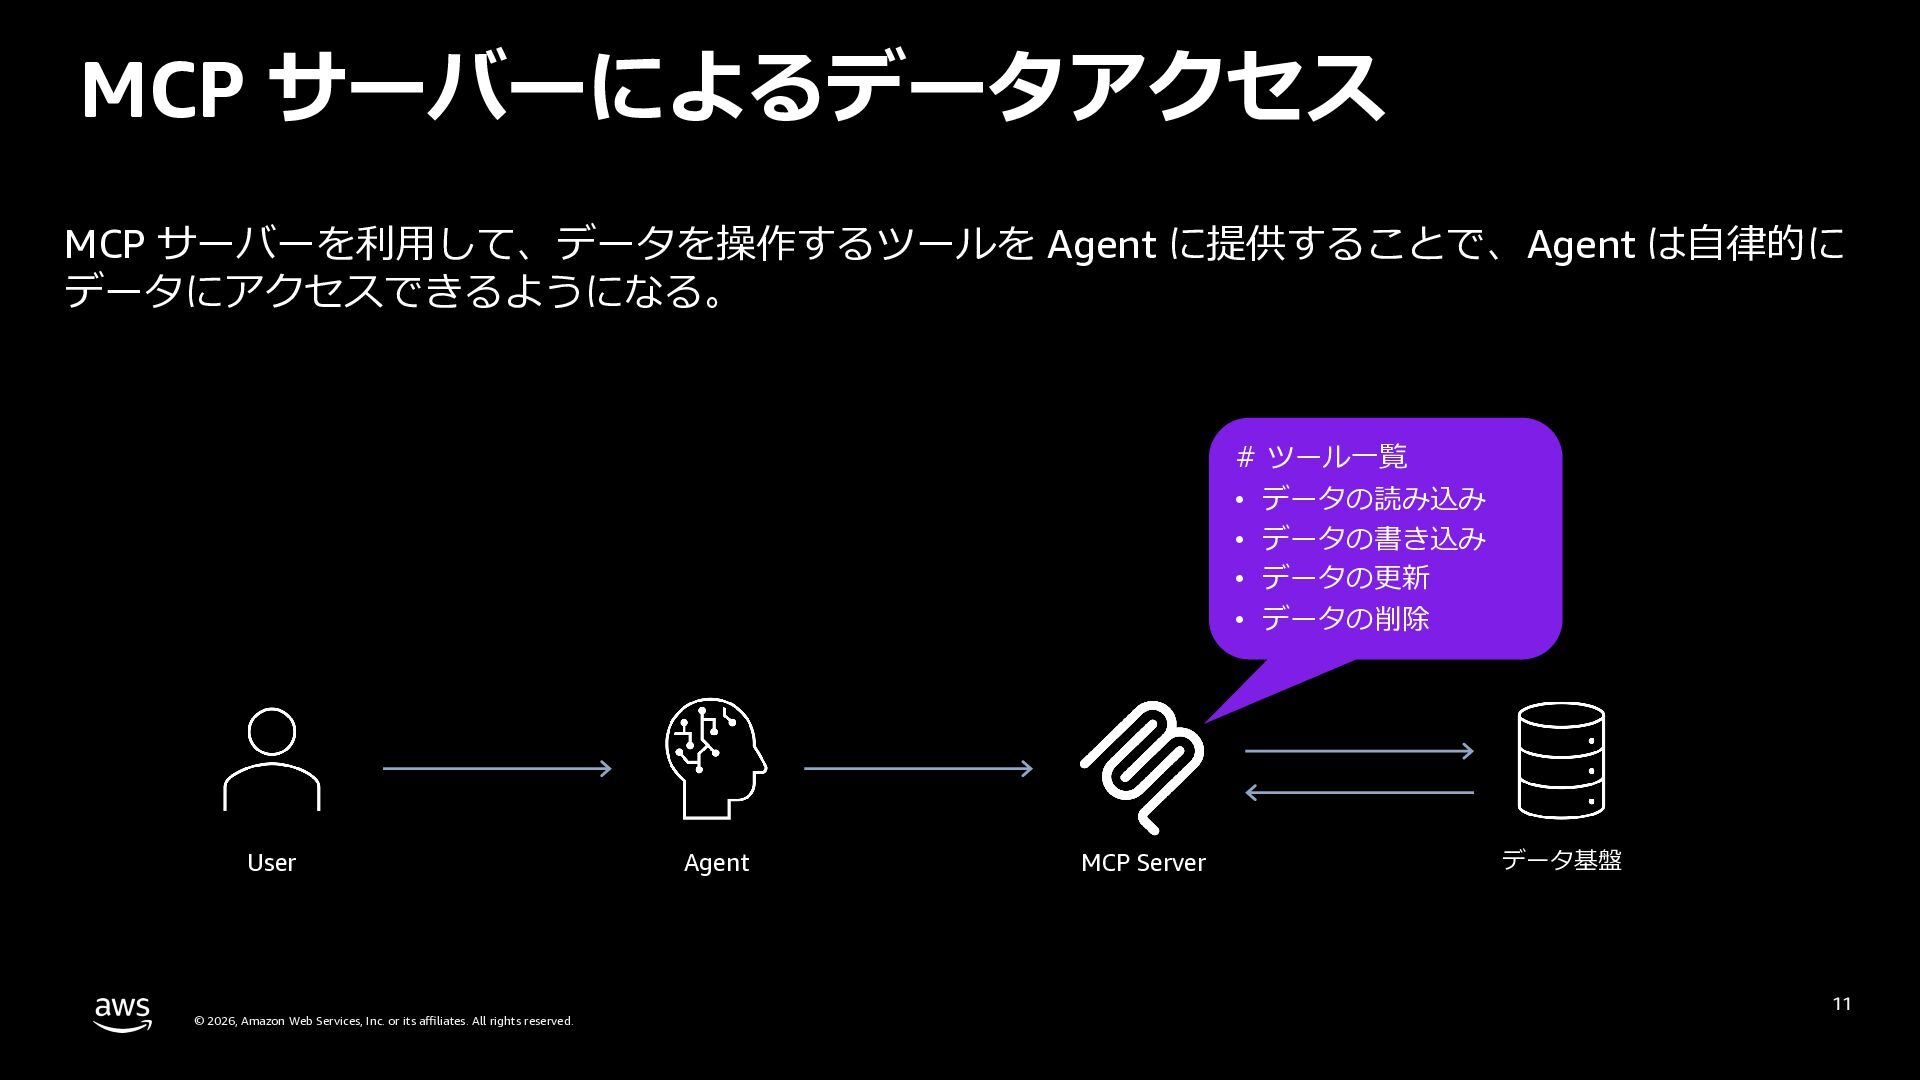
  10. MCP サーバーによるデータアクセス MCP サーバーを利⽤して、データを操作するツールを Agent に提供することで、Agent は⾃律的に データにアクセスできるようになる。 # ツール⼀覧

    • データの読み込み • データの書き込み • データの更新 • データの削除 User © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Agent MCP Server データ基盤 11
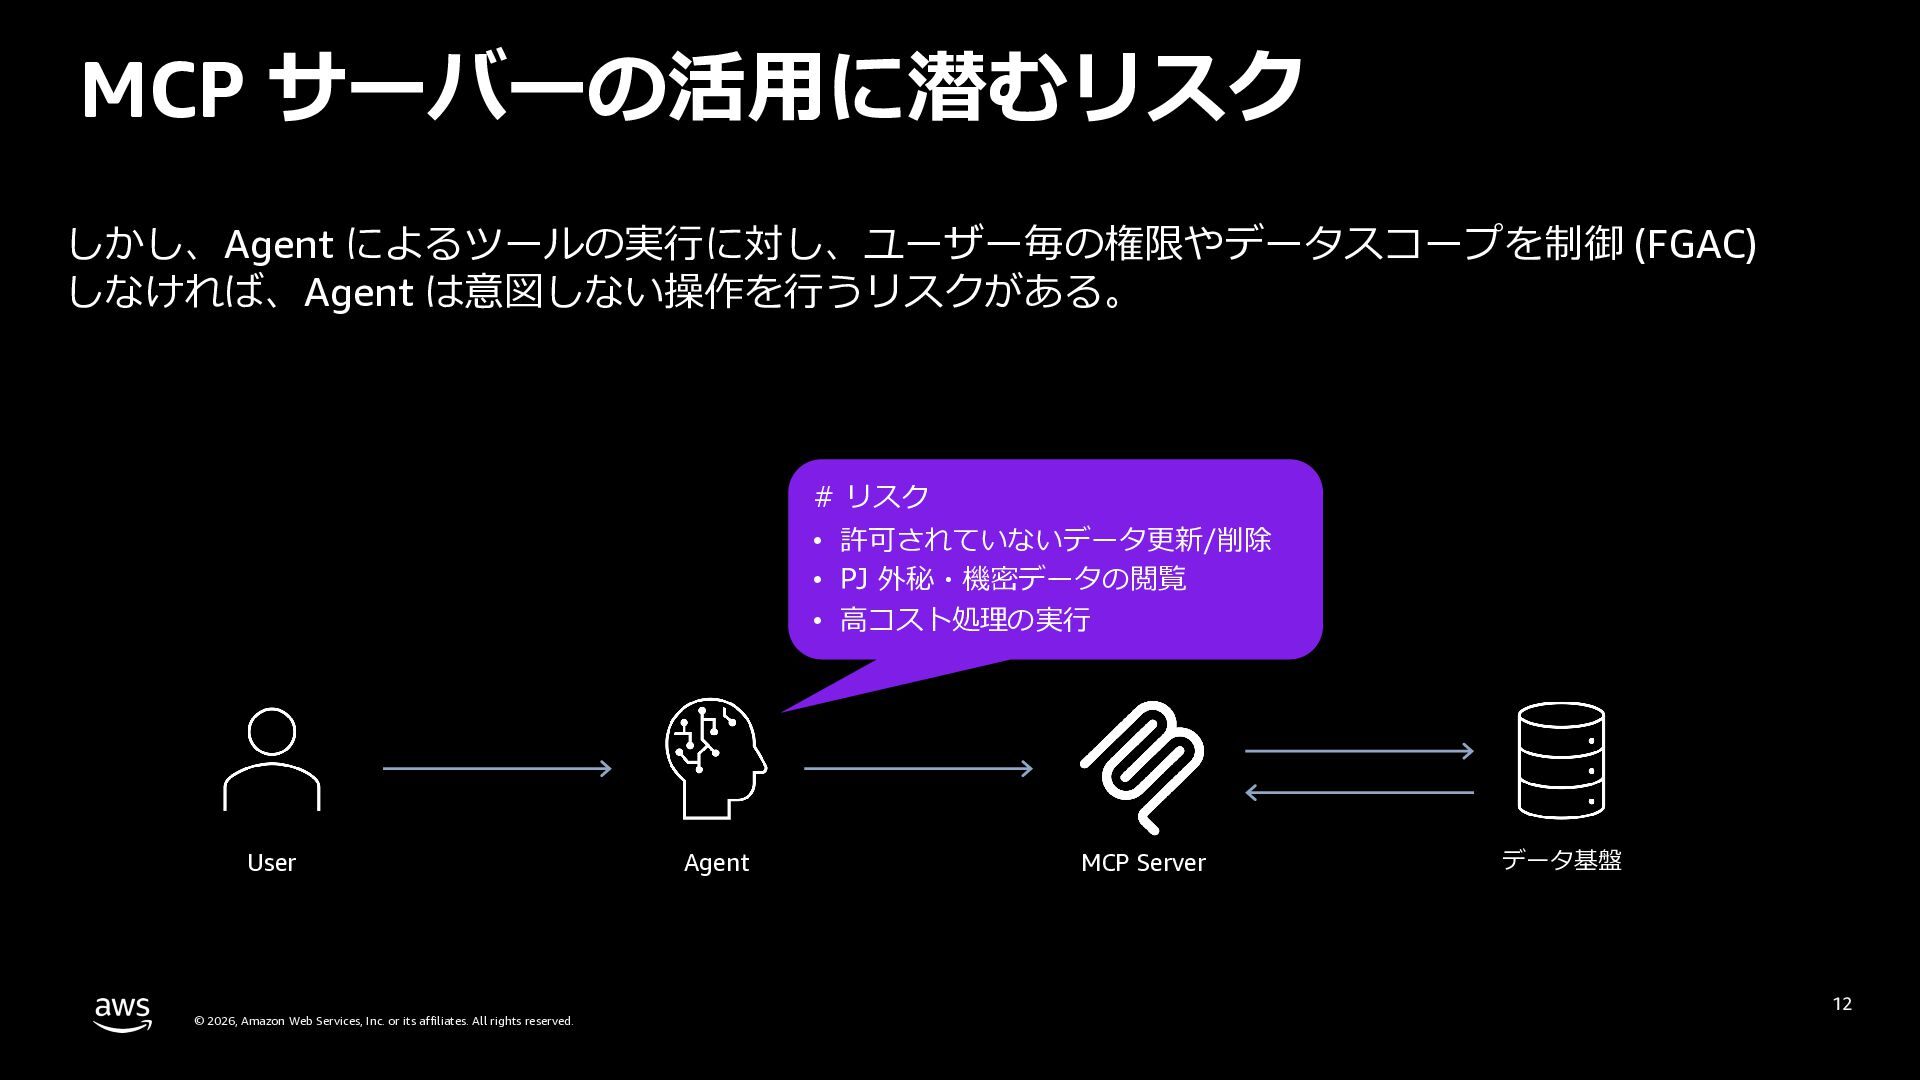
  11. MCP サーバーの活⽤に潜むリスク しかし、Agent によるツールの実⾏に対し、ユーザー毎の権限やデータスコープを制御 (FGAC) しなければ、Agent は意図しない操作を⾏うリスクがある。 # リスク •

    許可されていないデータ更新/削除 • PJ 外秘・機密データの閲覧 • ⾼コスト処理の実⾏ User © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Agent MCP Server データ基盤 12
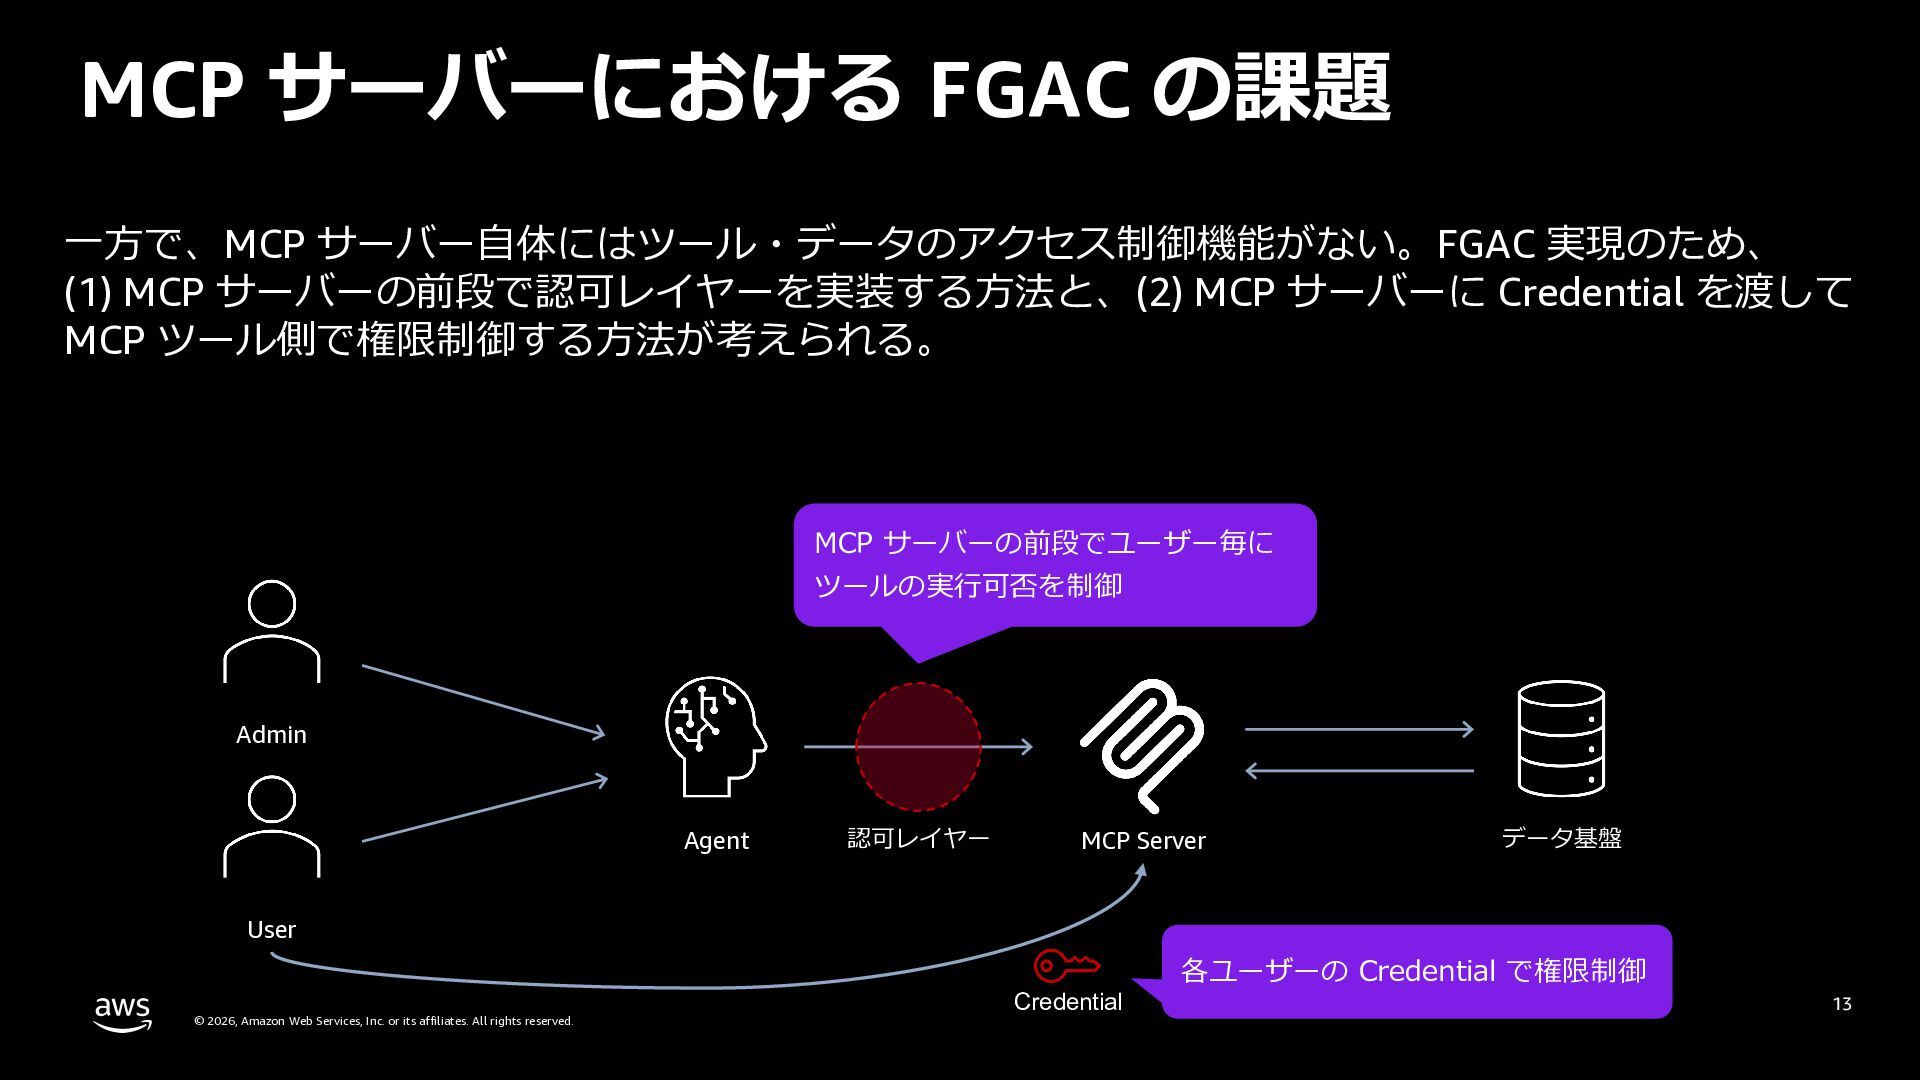
  12. MCP サーバーにおける FGAC の課題 ⼀⽅で、MCP サーバー⾃体にはツール・データのアクセス制御機能がない。FGAC 実現のため、 (1) MCP サーバーの前段で認可レイヤーを実装する⽅法と、(2)

    MCP サーバーに Credential を渡して MCP ツール側で権限制御する⽅法が考えられる。 MCP サーバーの前段でユーザー毎に ツールの実⾏可否を制御 Admin Agent 認可レイヤー MCP Server データ基盤 User © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Credential 各ユーザーの Credential で権限制御 13
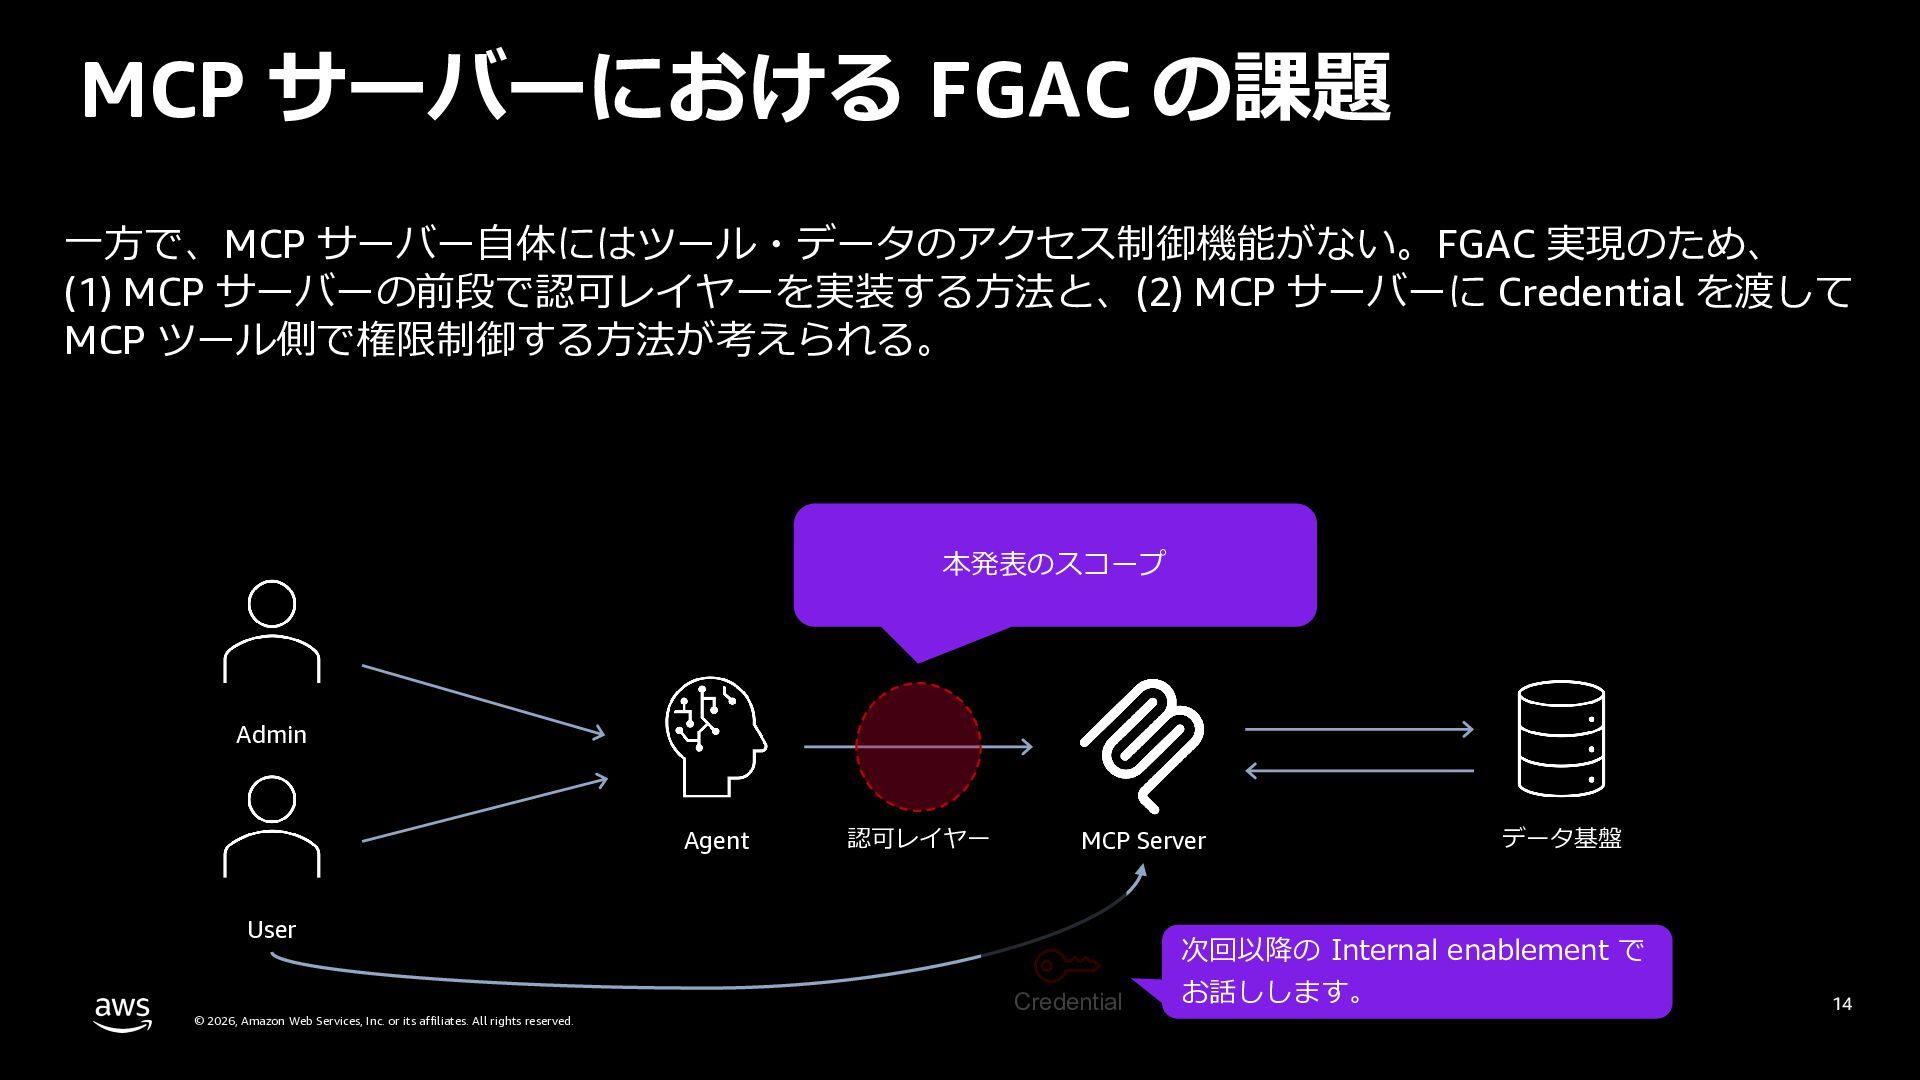
  13. MCP サーバーにおける FGAC の課題 ⼀⽅で、MCP サーバー⾃体にはツール・データのアクセス制御機能がない。FGAC 実現のため、 (1) MCP サーバーの前段で認可レイヤーを実装する⽅法と、(2)

    MCP サーバーに Credential を渡して MCP ツール側で権限制御する⽅法が考えられる。 本発表のスコープ Admin Agent 認可レイヤー MCP Server データ基盤 User © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Credential 本 Enablement の後編で解説します。 14
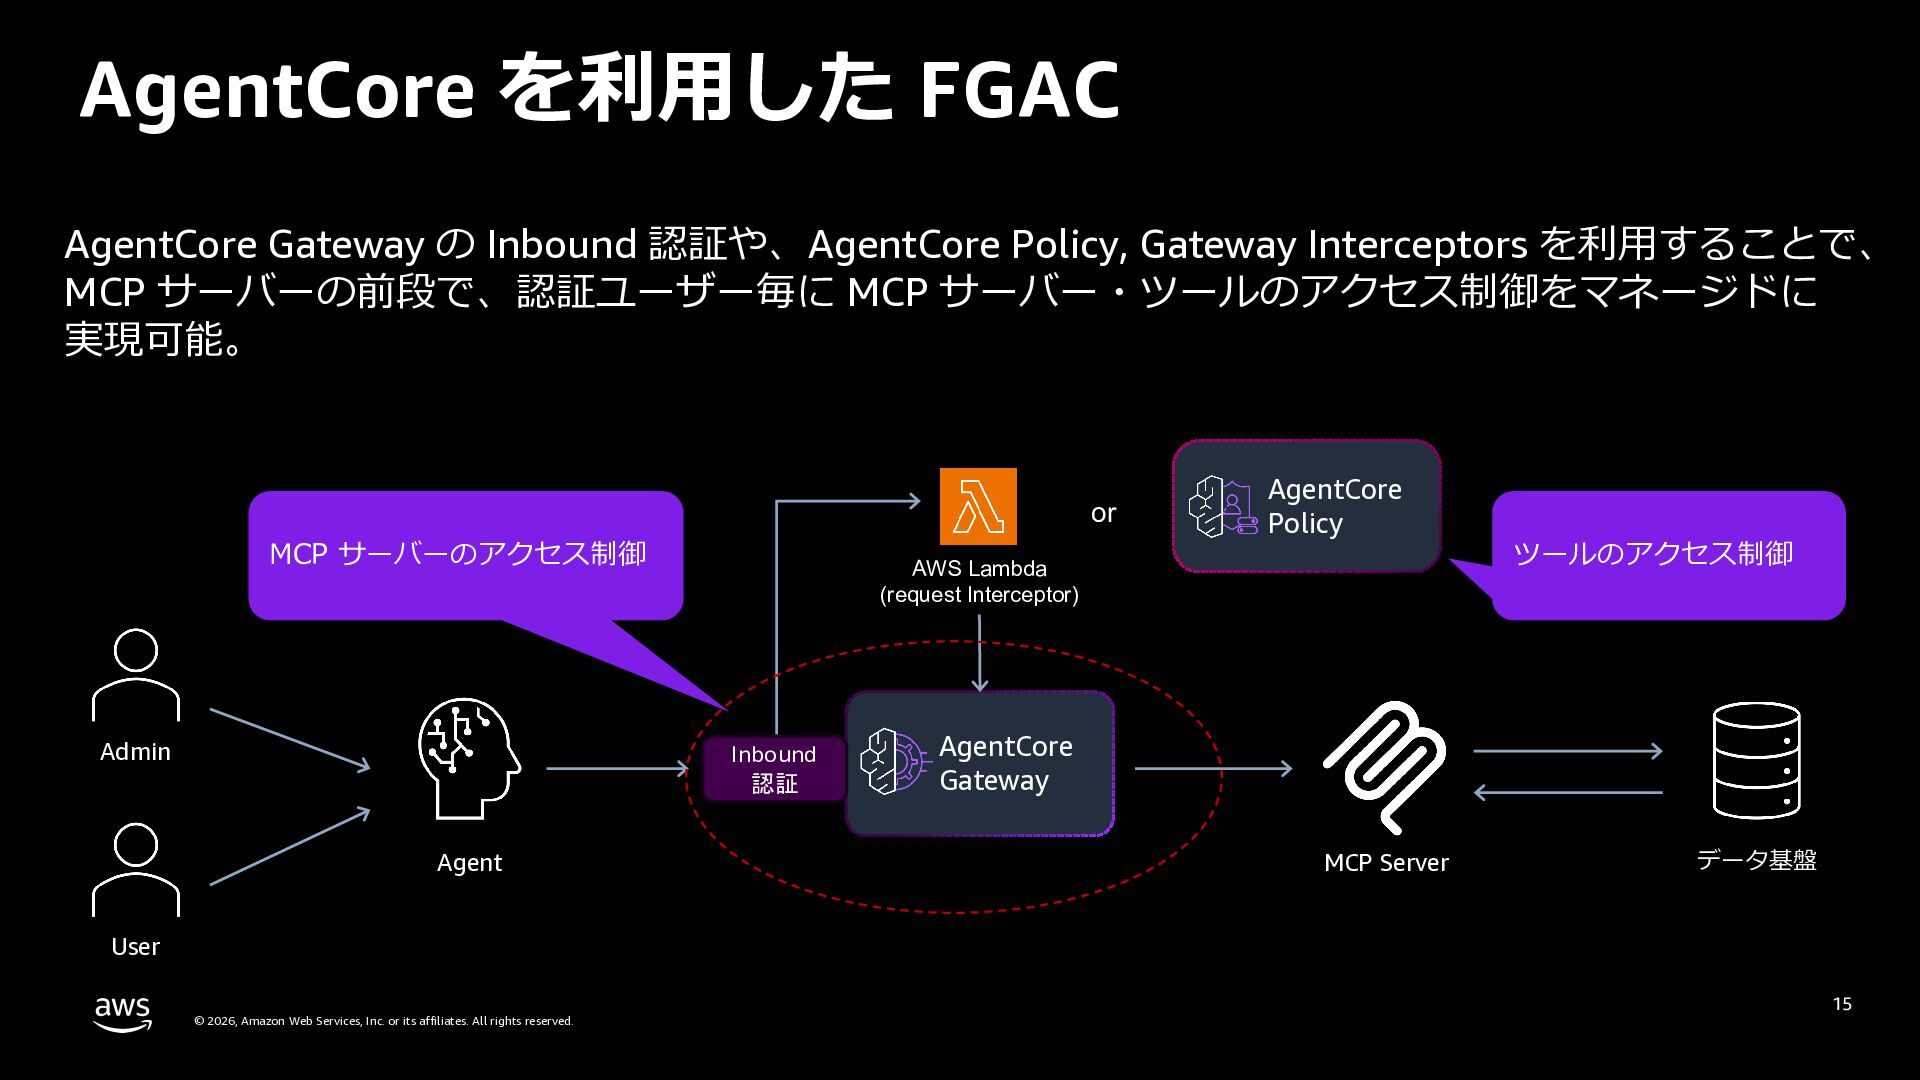
  14. AgentCore を利⽤した FGAC AgentCore Gateway の Inbound 認証や、AgentCore Policy, Gateway

    Interceptors を利⽤することで、 MCP サーバーの前段で、認証ユーザー毎に MCP サーバー・ツールのアクセス制御をマネージドに 実現可能。 or MCP サーバーのアクセス制御 Admin AWS Lambda (request Interceptor) Inbound 認証 Agent AgentCore Policy ツールのアクセス制御 AgentCore Gateway MCP Server データ基盤 User © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 15
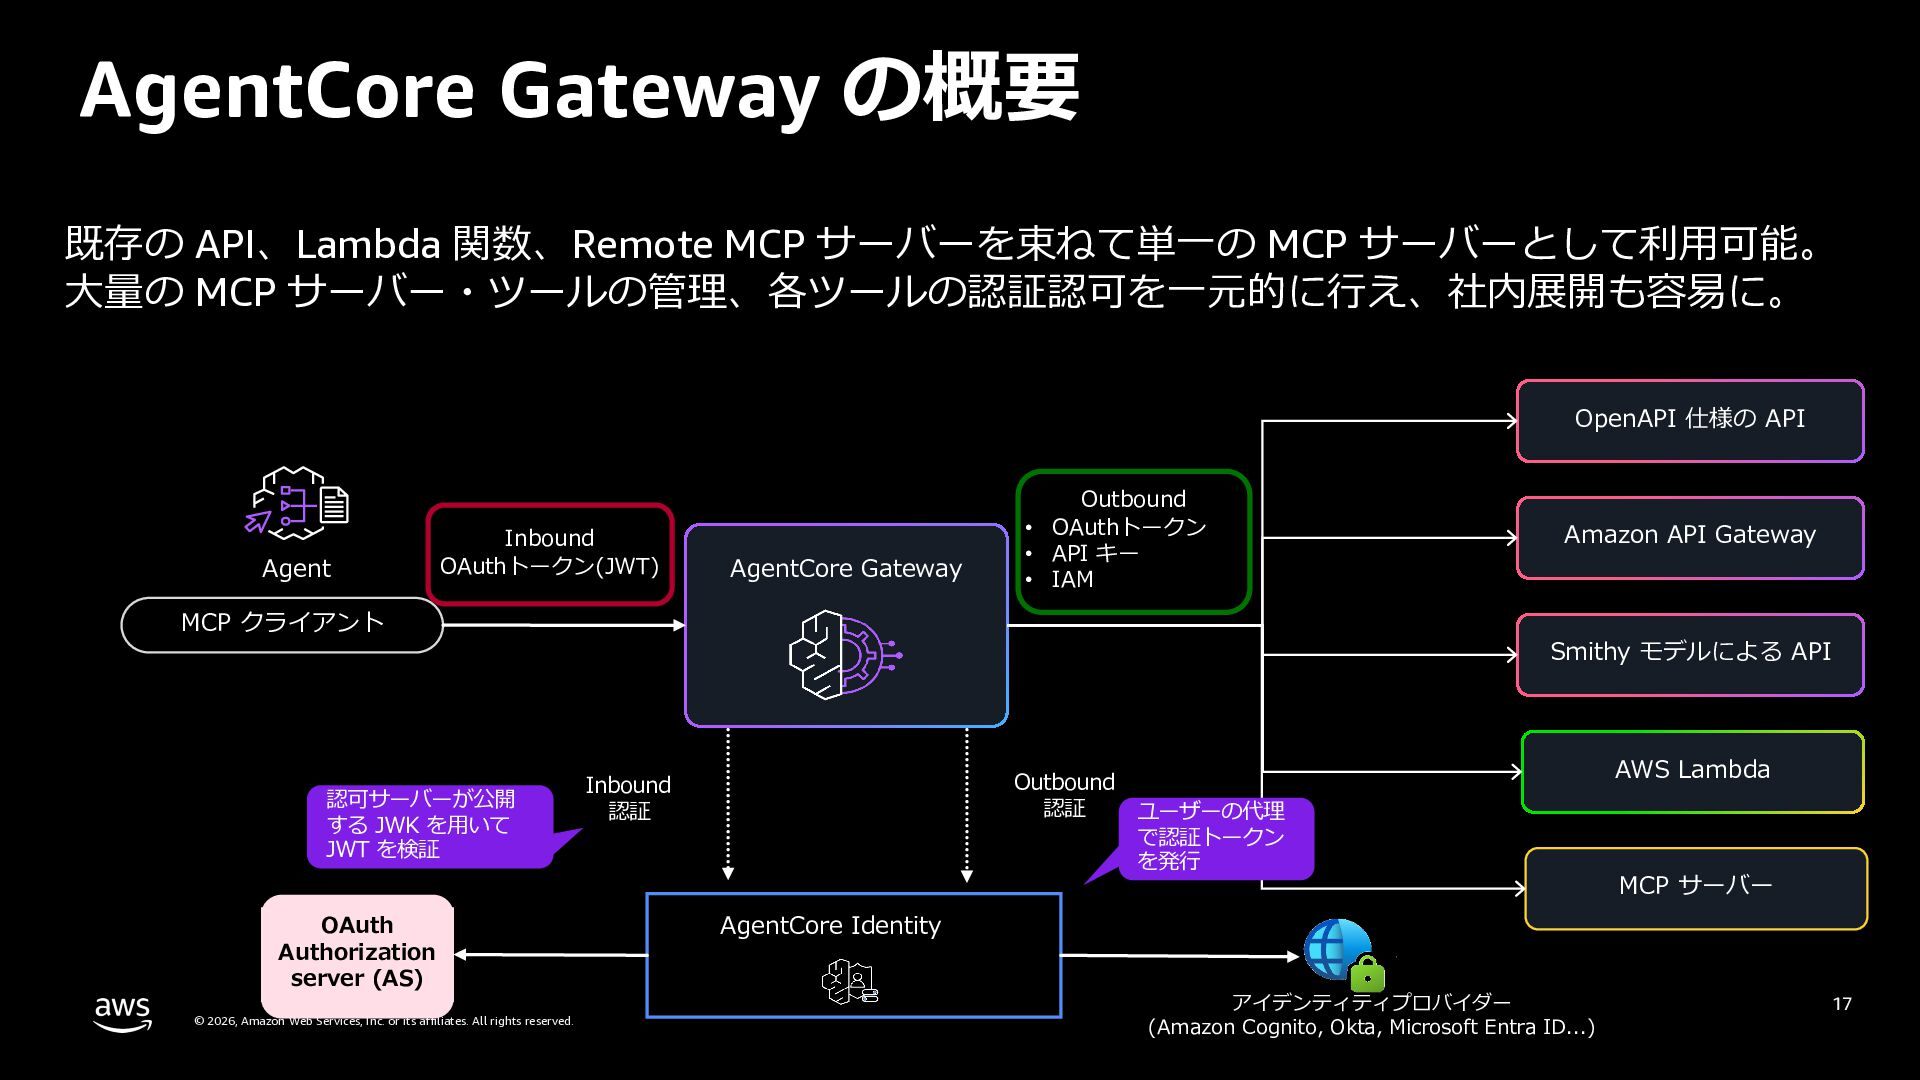
  15. AgentCore Gateway の概要 既存の API、Lambda 関数、Remote MCP サーバーを束ねて単⼀の MCP サーバーとして利⽤可能。

    ⼤量の MCP サーバー・ツールの管理、各ツールの認証認可を⼀元的に⾏え、社内展開も容易に。 OpenAPI 仕様の API Agent Inbound OAuthトークン(JWT) AgentCore Gateway Outbound • OAuthトークン • API キー • IAM MCP クライアント 認可サーバーが公開 する JWK を⽤いて JWT を検証 OAuth Authorization server (AS) © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Amazon API Gateway Smithy モデルによる API Outbound 認証 ユーザーの代理 で認証トークン を発⾏ Inbound 認証 AWS Lambda MCP サーバー AgentCore Identity アイデンティティプロバイダー (Amazon Cognito, Okta, Microsoft Entra ID...) 17
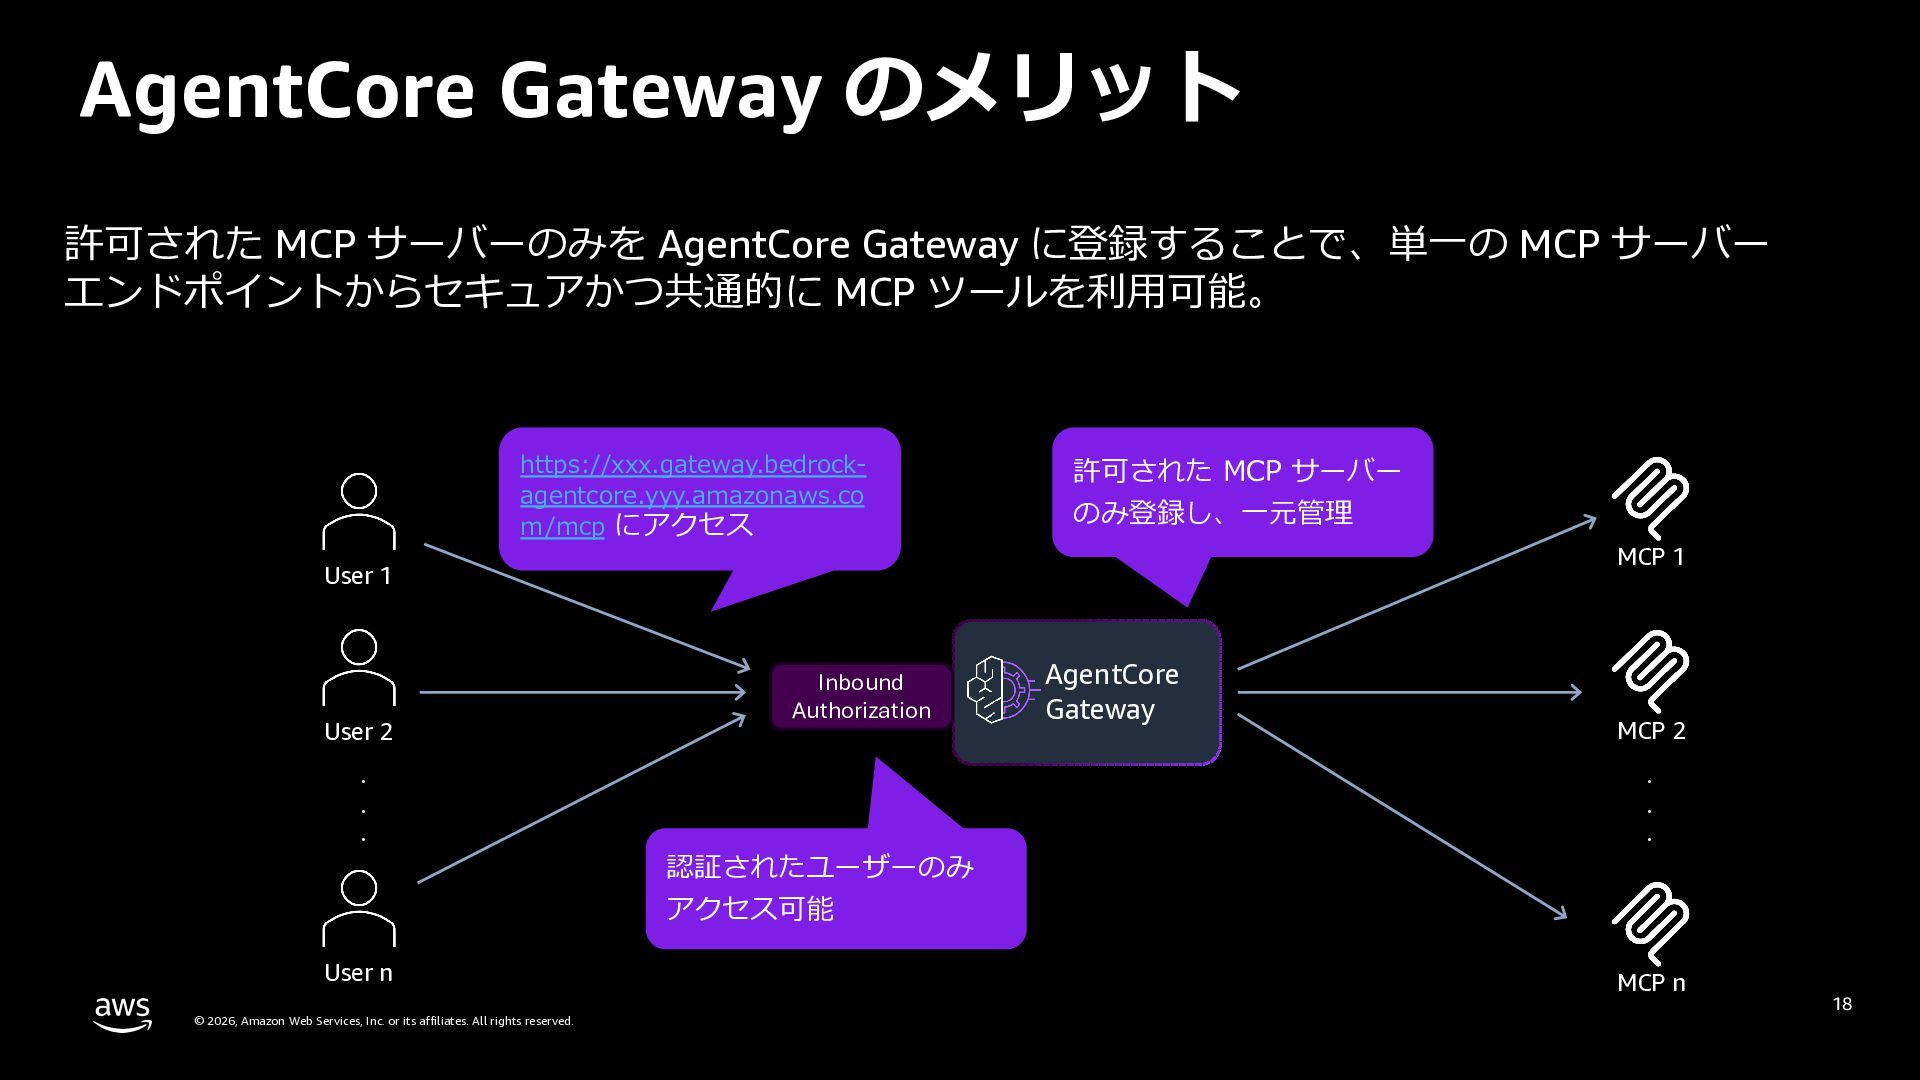
  16. AgentCore Gateway のメリット 許可された MCP サーバーのみを AgentCore Gateway に登録することで、単⼀の MCP

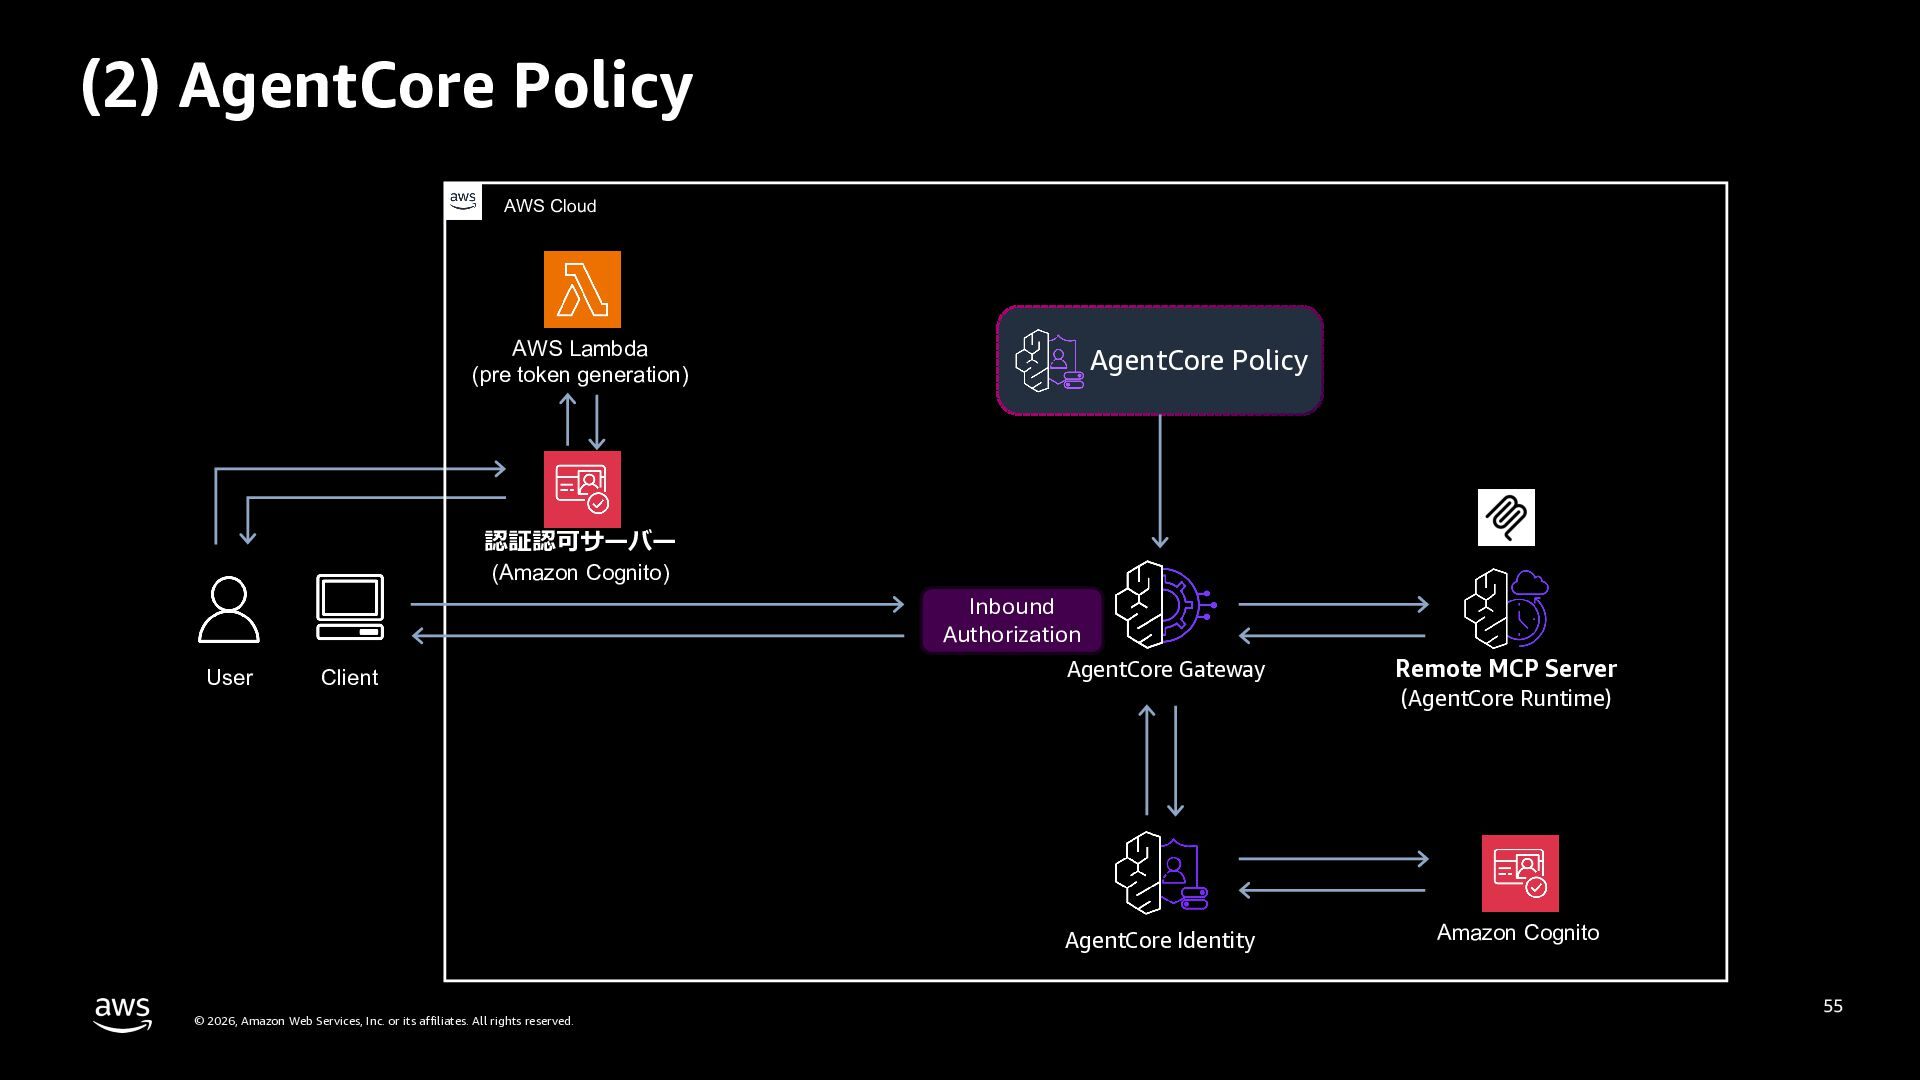
    サーバー エンドポイントからセキュアかつ共通的に MCP ツールを利⽤可能。 https://xxx.gateway.bedrockagentcore.yyy.amazonaws.co m/mcp にアクセス 許可された MCP サーバー のみ登録し、⼀元管理 MCP 1 User 1 User 2 Inbound Authorization . . . AgentCore Gateway MCP 2 . . . 認証されたユーザーのみ アクセス可能 User n © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. MCP n 18
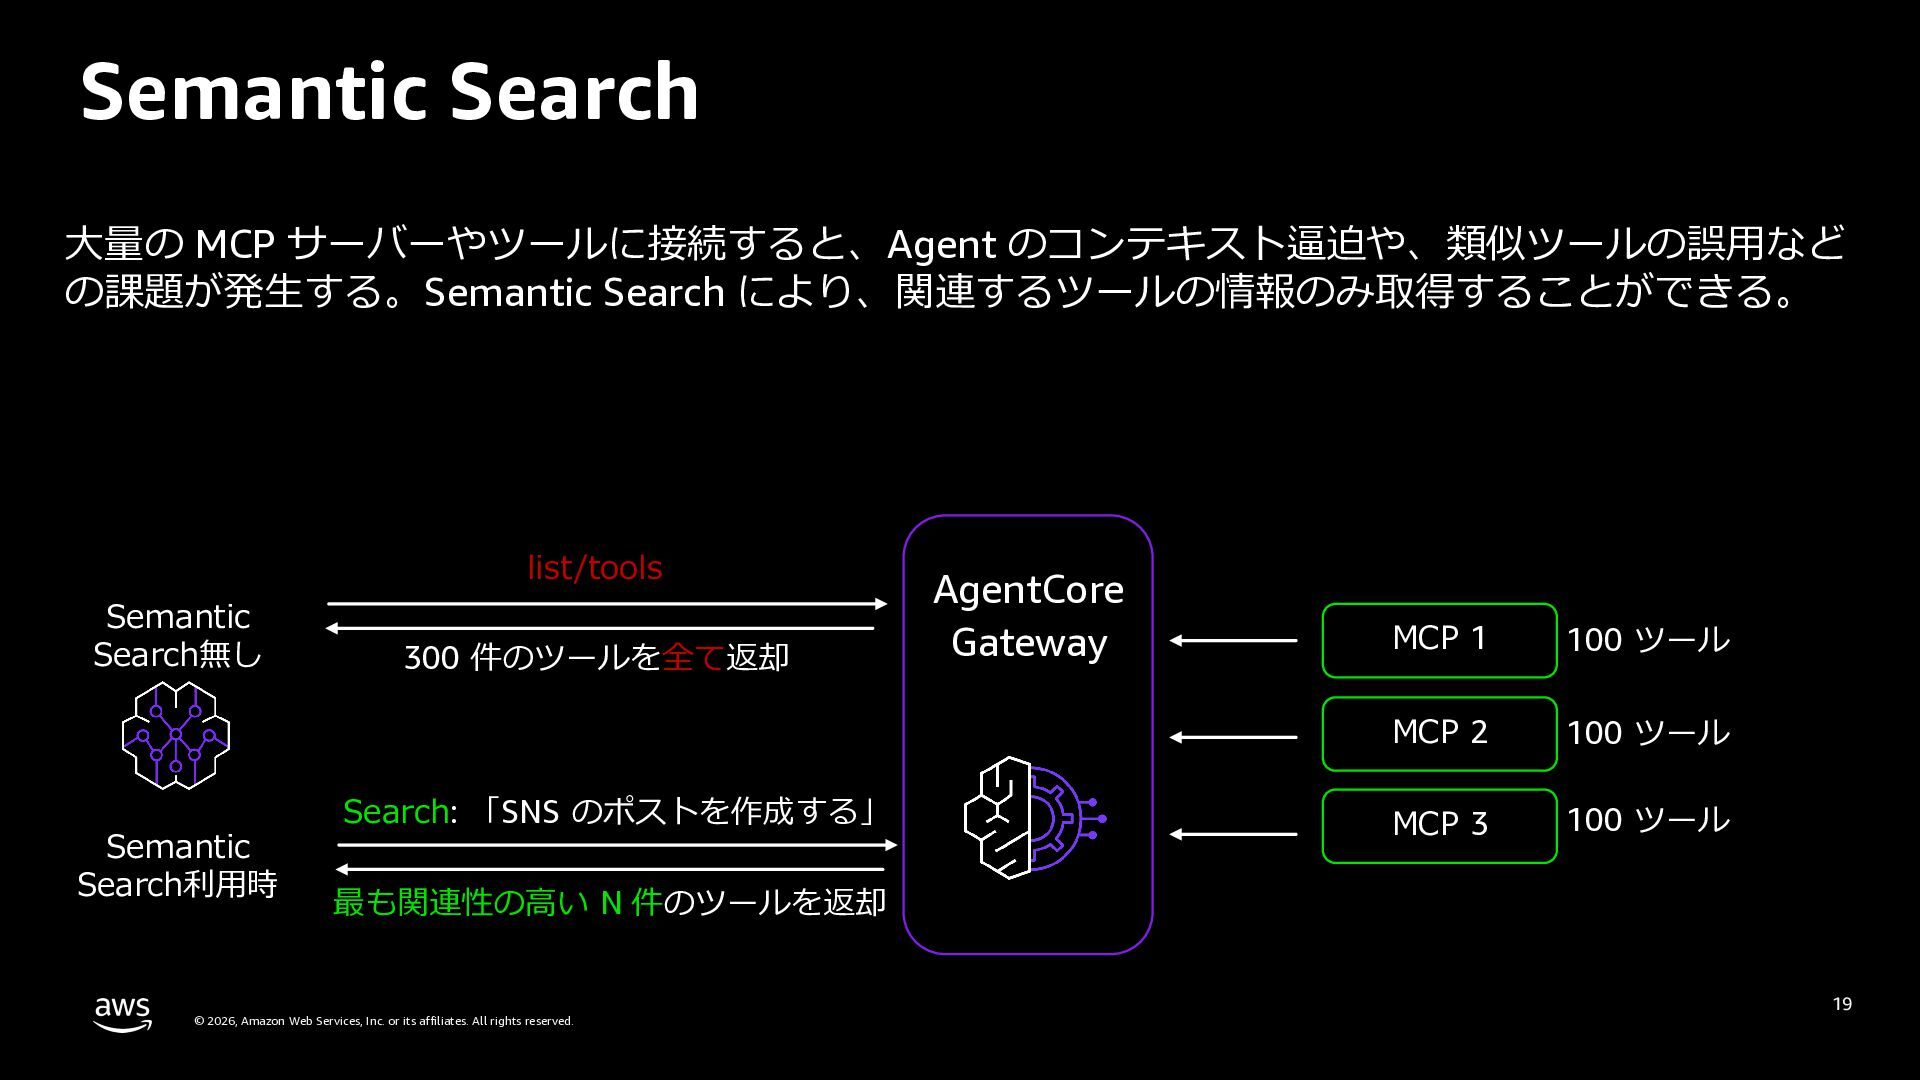
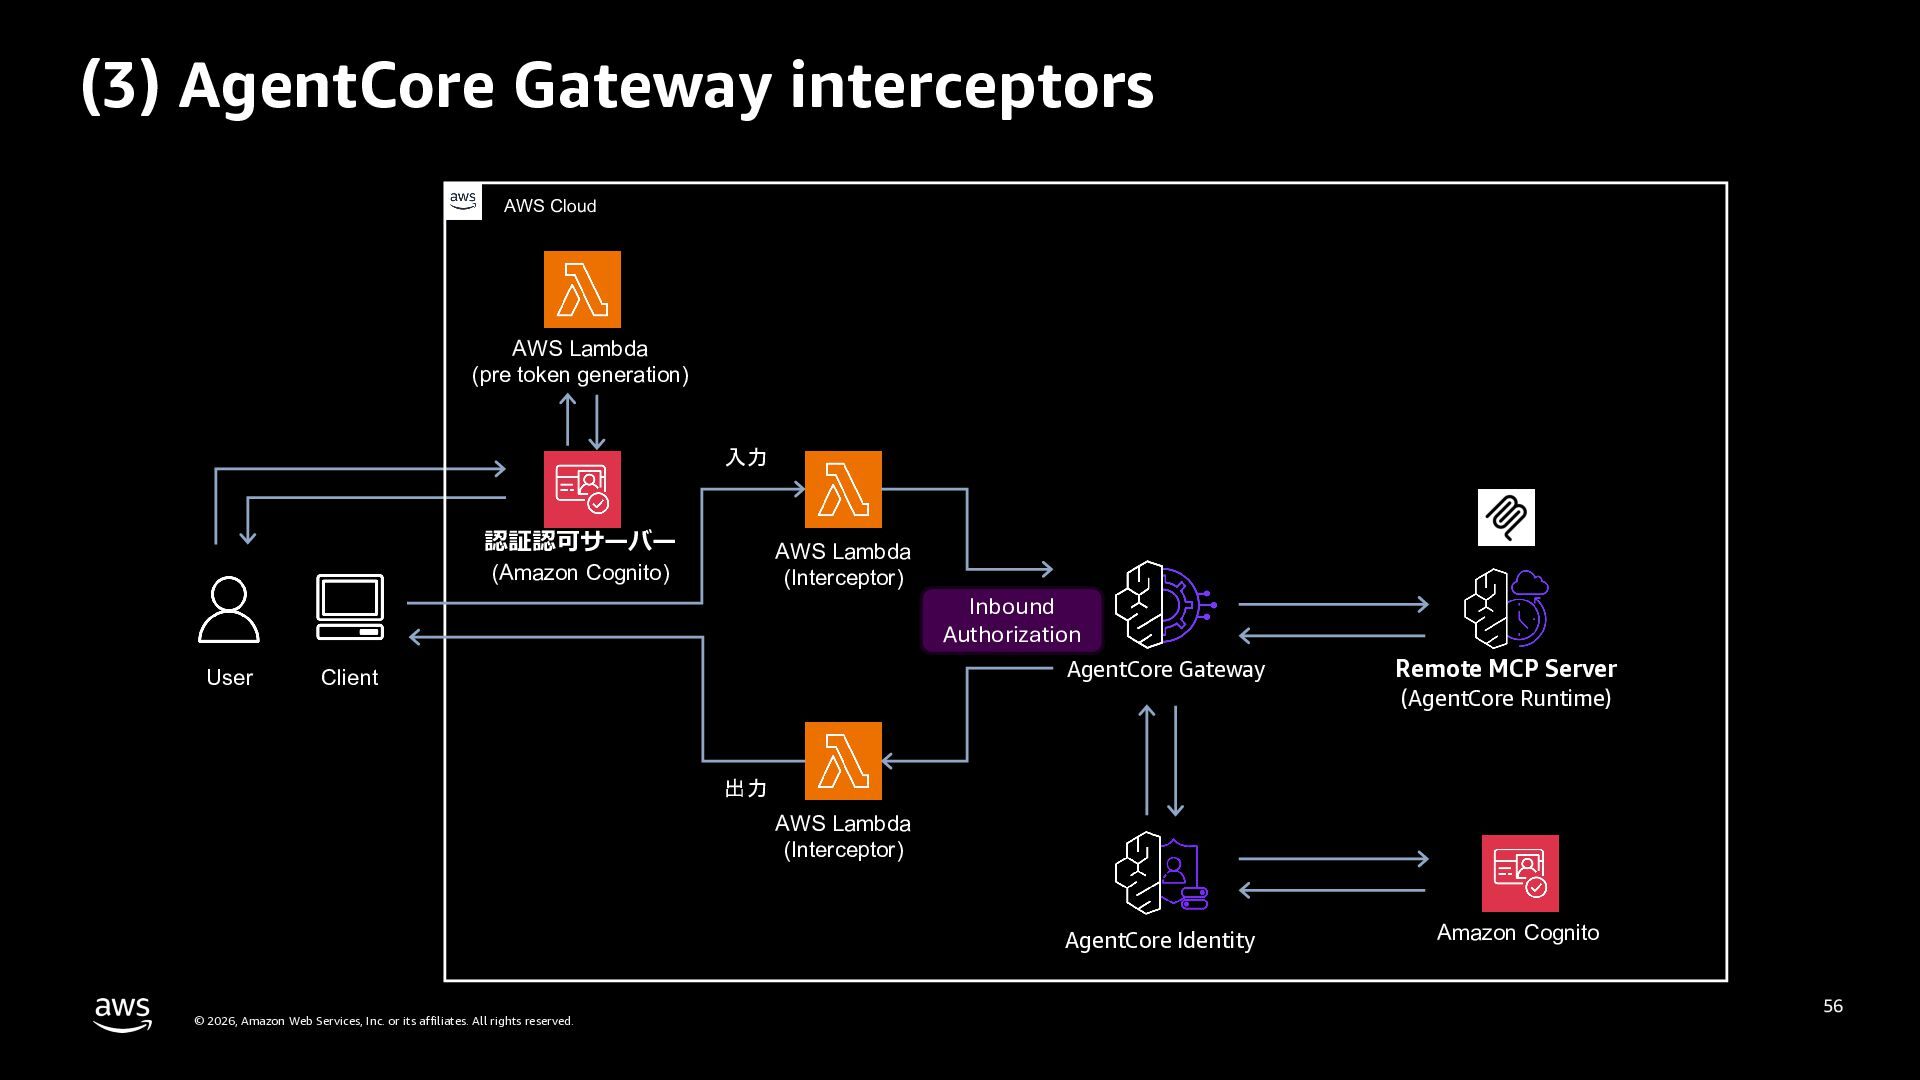
  17. Semantic Search Agent が⼤量の MCP サーバーやツールに接続すると、Agent のコンテキスト逼迫や、類似ツールの 誤⽤などの課題が発⽣する。Semantic Search により、関連するツールの情報のみ取得できる。
    list/tools Semantic Search無し Semantic Search利⽤時 300 件のツールを全て返却 Search: 「SNS のポストを作成する」 AgentCore Gateway MCP 1 100 ツール MCP 2 100 ツール MCP 3 100 ツール 最も関連性の⾼い N 件のツールを返却 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 19
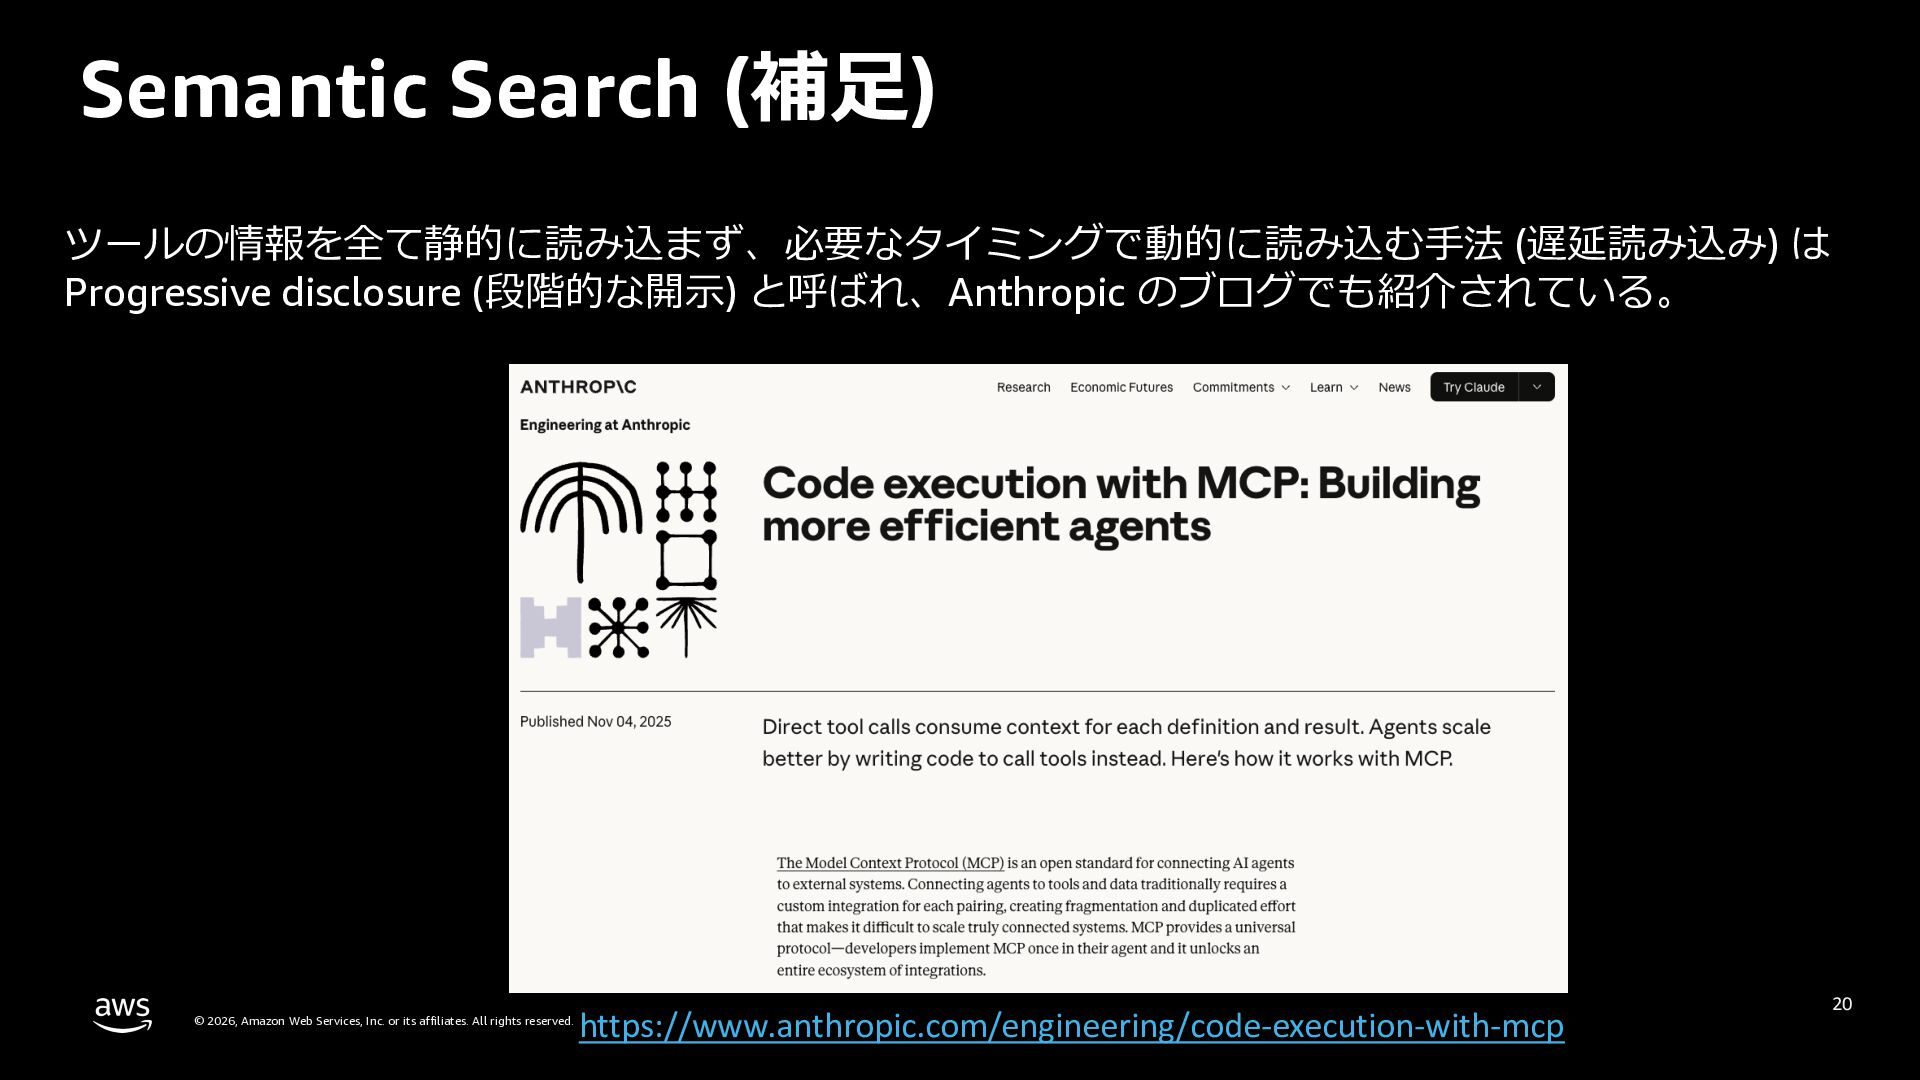
  18. Semantic Search (補⾜) ツールの情報を全て静的に読み込まず、必要なタイミングで動的に読み込む⼿法 (遅延読み込み) は Progressive disclosure (段階的な開⽰) と呼ばれ、Anthropic

    のブログでも紹介されている。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. https://www.anthropic.com/engineering/code-execution-with-mcp 20
  19. AgentCore Gateway における MCP サーバー / ツールのアクセス 制御⽅法 © 2026,

    Amazon Web Services, Inc. or its affiliates. All rights reserved. 21
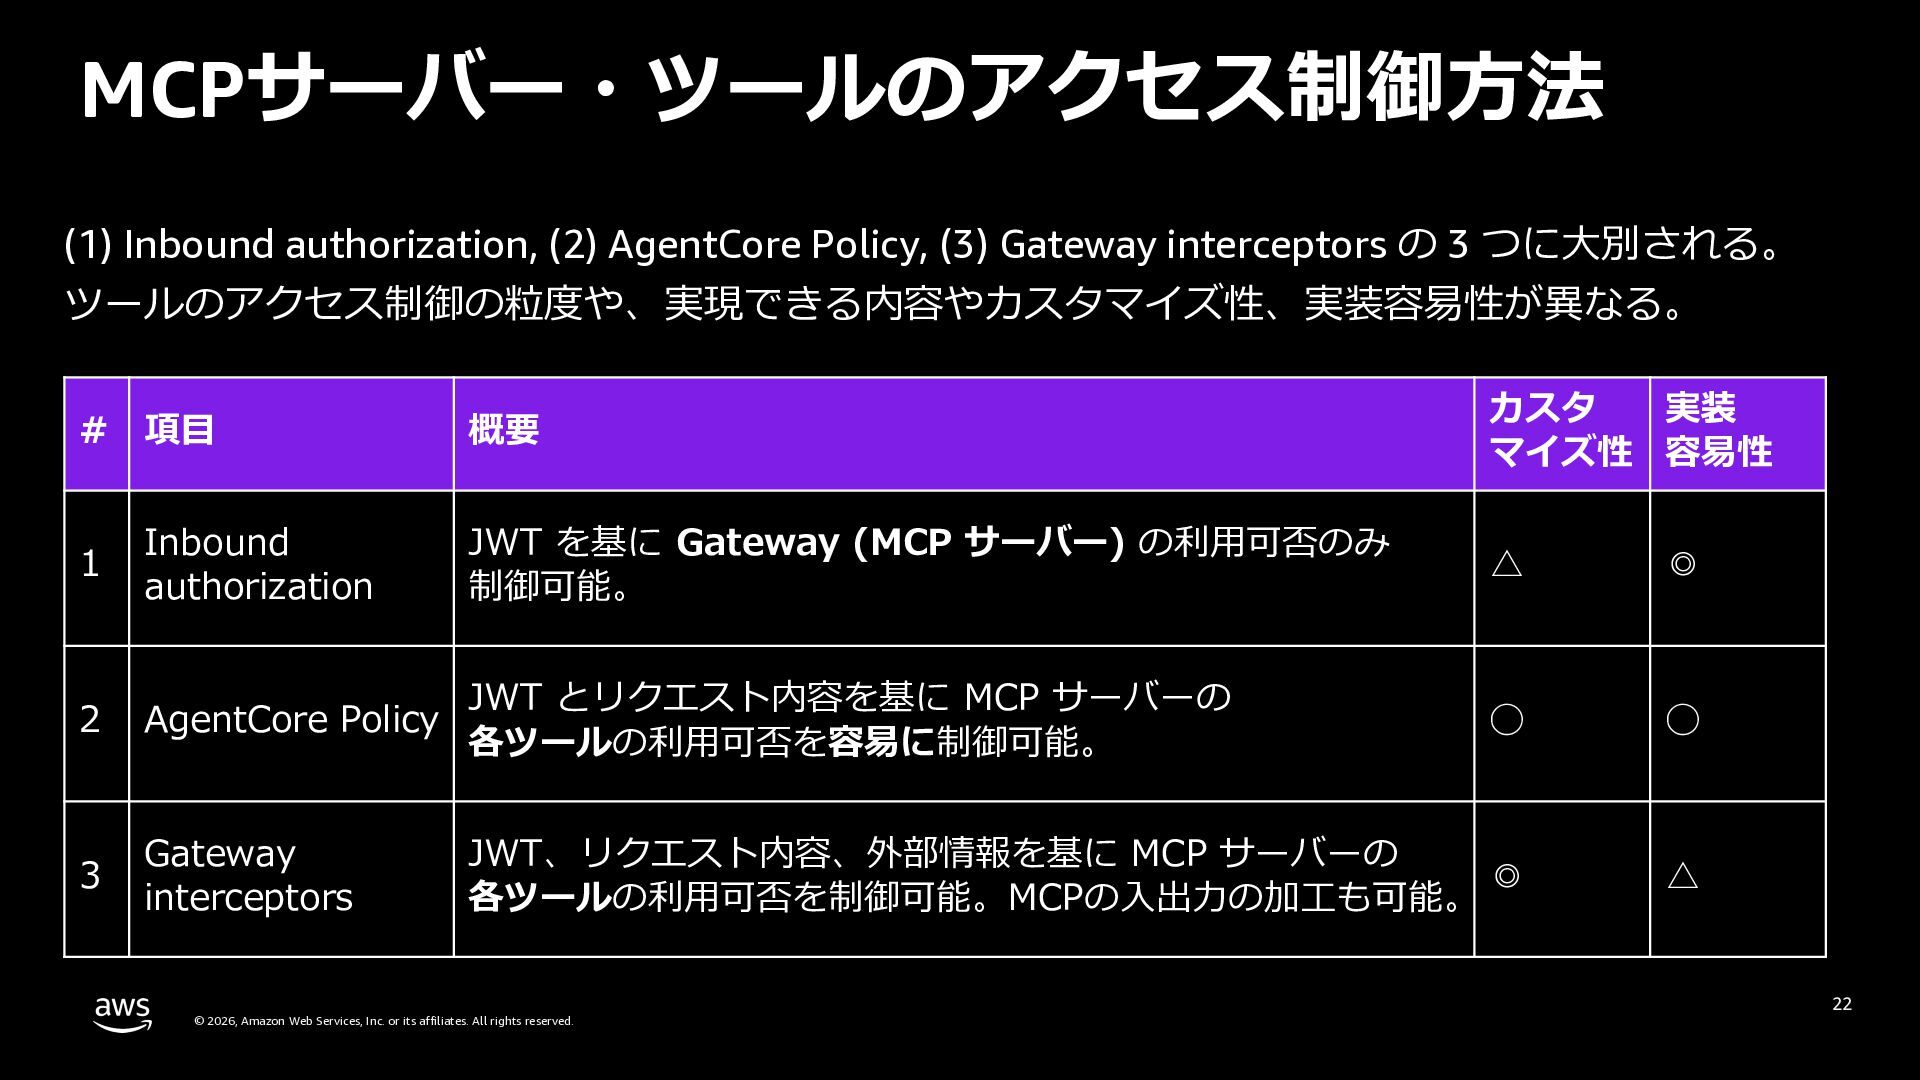
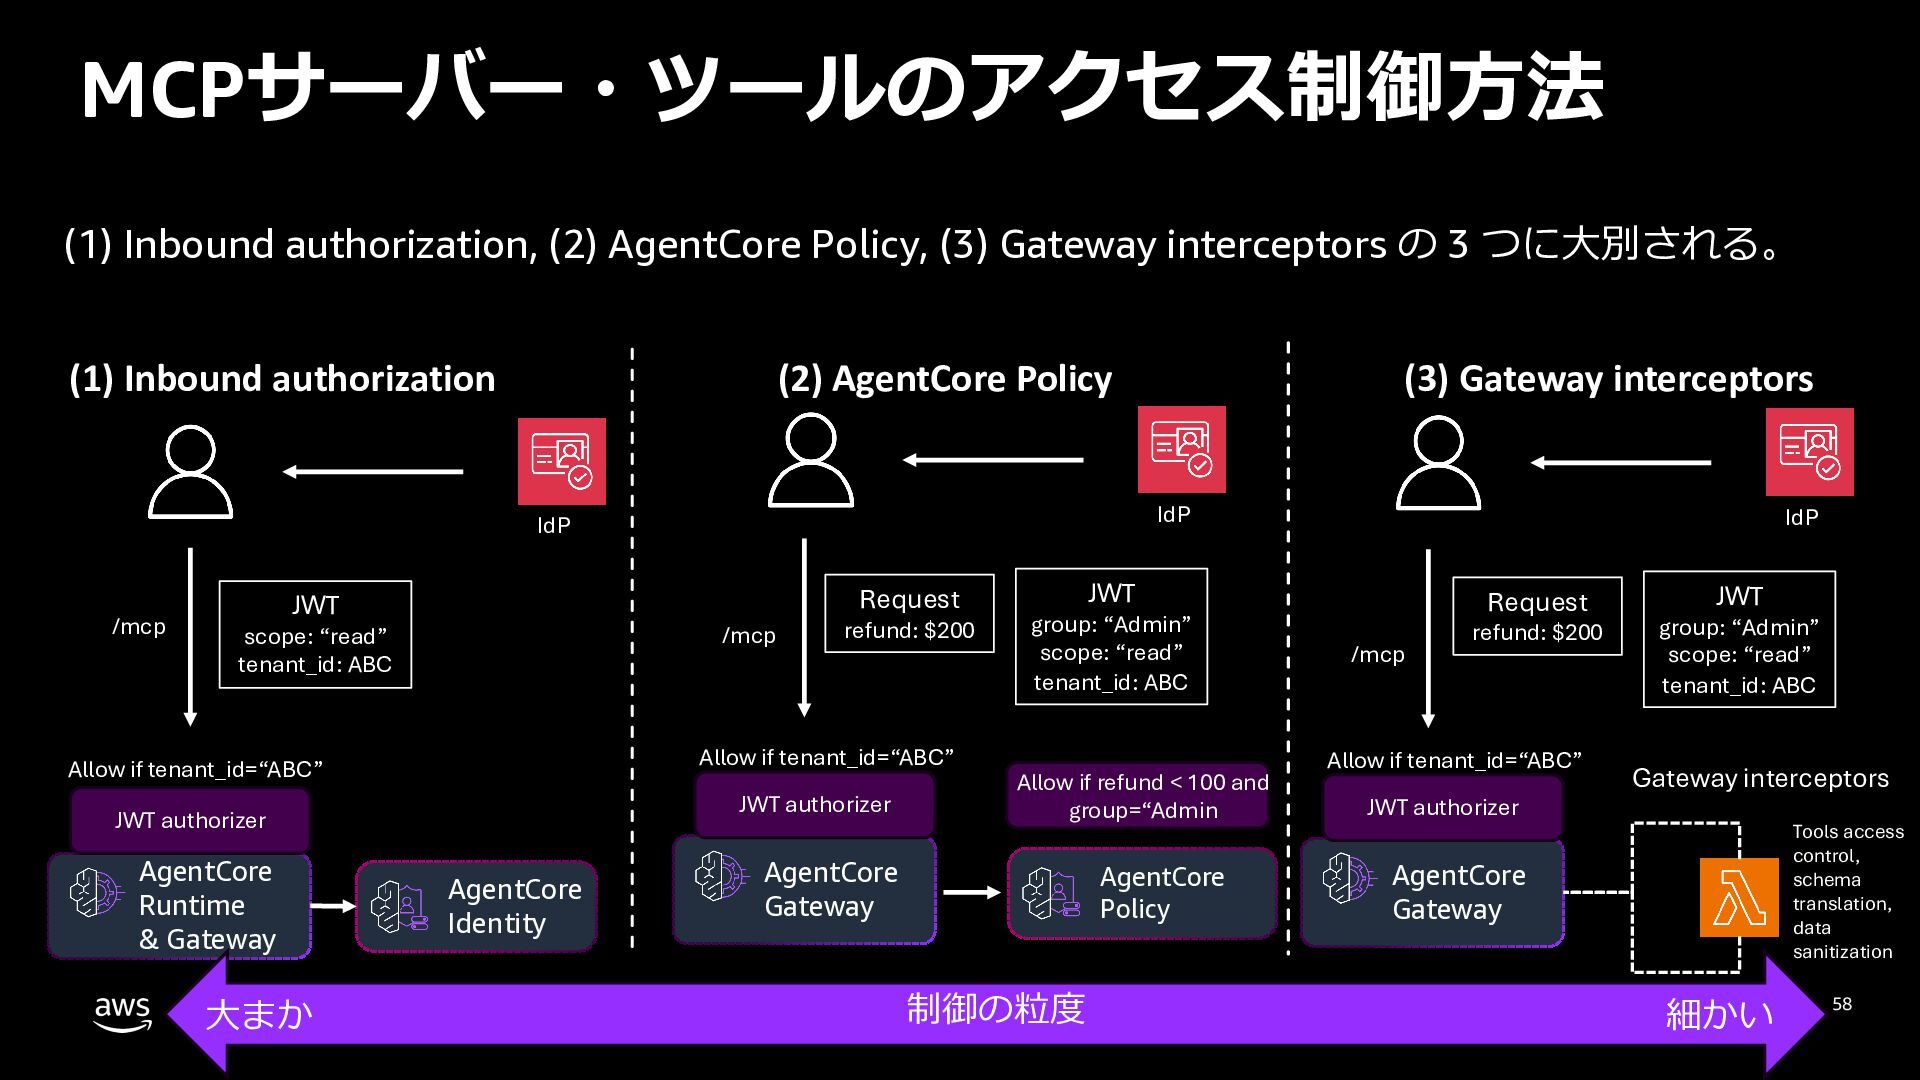
  20. MCPサーバー・ツールのアクセス制御⽅法 (1) Inbound authorization, (2) AgentCore Policy, (3) Gateway interceptors

    の 3 つに⼤別される。 ツールのアクセス制御の粒度や、実現できる内容やカスタマイズ性、実装容易性が異なる。 # 項⽬ 概要 カスタ 実装 マイズ性 容易性 1 Inbound authorization JWT を基に Gateway (MCP サーバー) の利⽤可否のみ 制御可能。 △ ◎ 2 AgentCore Policy JWT とリクエスト内容を基に MCP サーバーの 各ツールの利⽤可否を容易に制御可能。 ◯ ◯ 3 Gateway interceptors JWT、リクエスト内容、外部情報を基に MCP サーバーの ◎ 各ツールの利⽤可否を制御可能。MCPの⼊出⼒の加⼯も可能。 △ © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 22
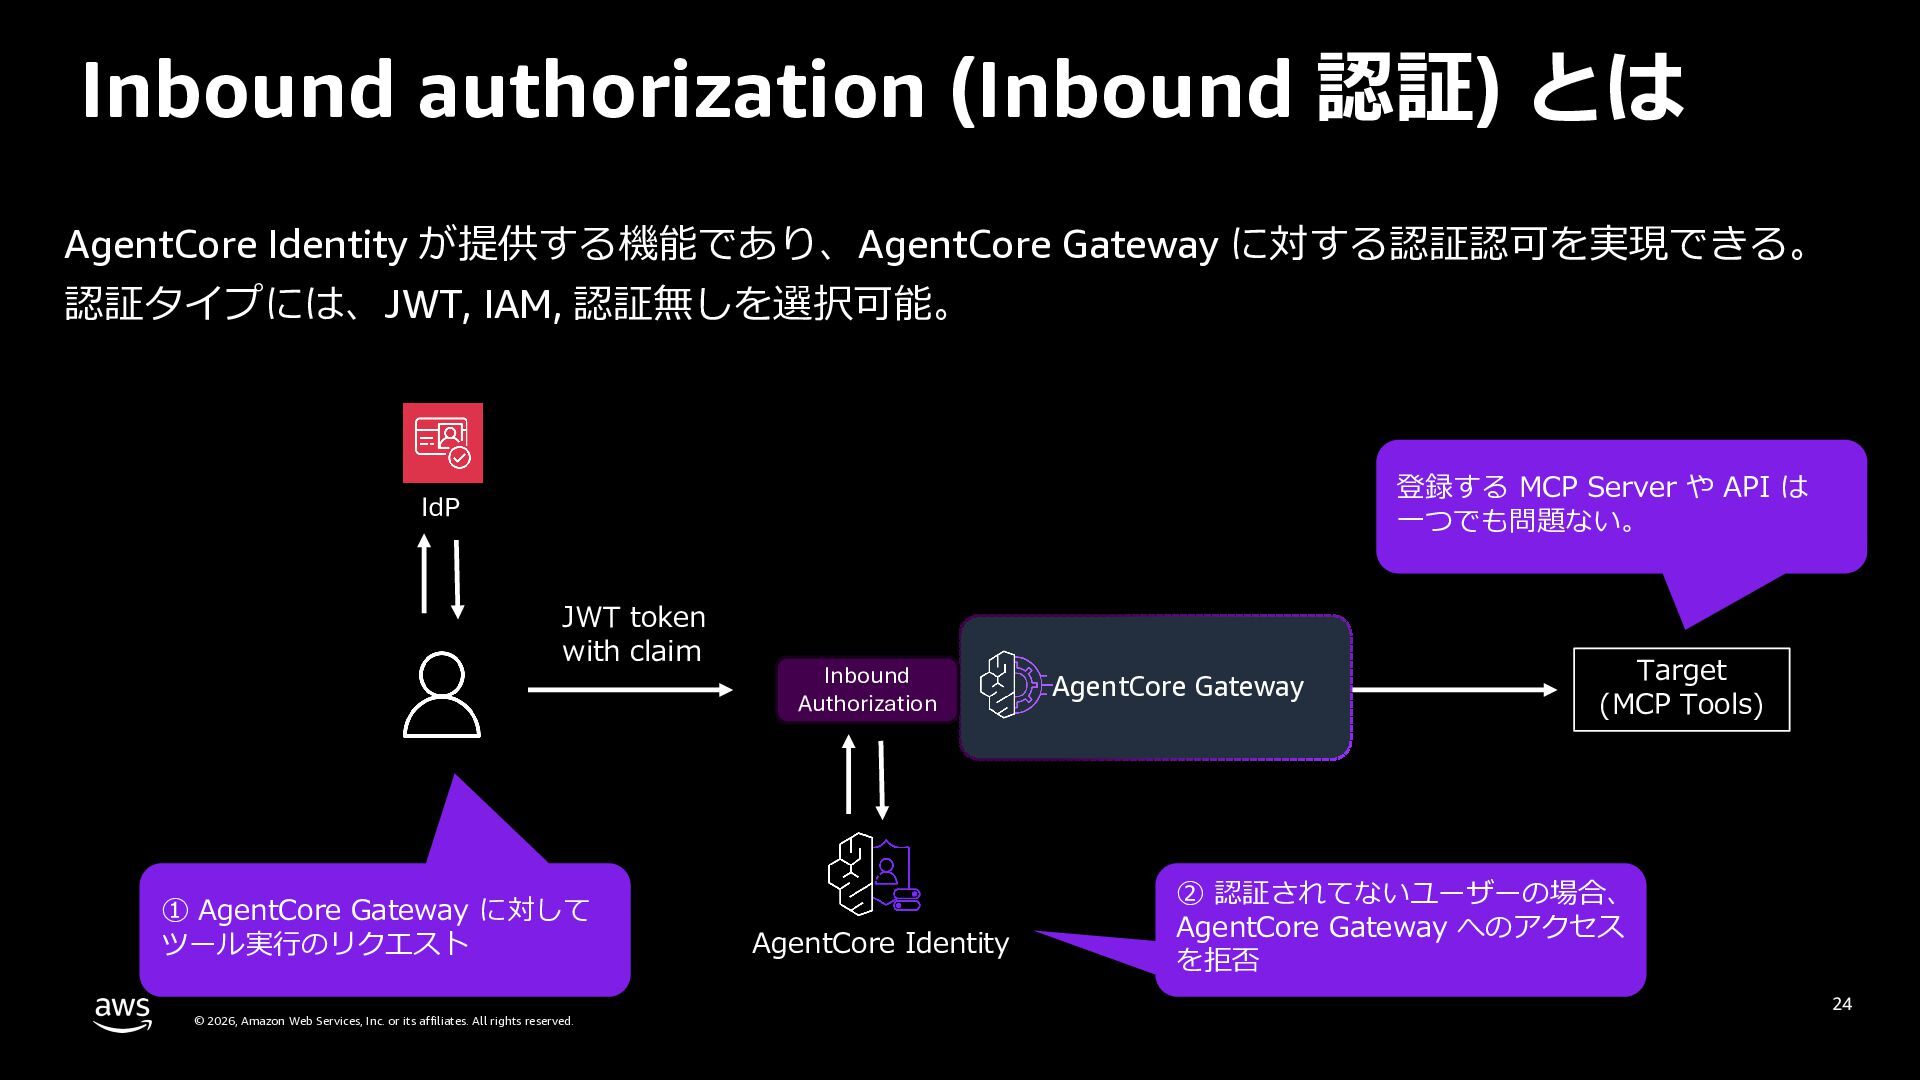
  21. Inbound authorization (Inbound 認証) とは AgentCore Identity が提供する機能であり、AgentCore Gateway に対する認証認可を実現できる。

    認証タイプには、JWT, IAM, 認証無しを選択可能。 登録する MCP Server や API は ⼀つでも問題ない。 IdP JWT token with claim ① AgentCore Gateway に対して ツール実⾏のリクエスト © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Inbound Authorization AgentCore Identity AgentCore Gateway Target (MCP Tools) ② 認証されてないユーザーの場合、 AgentCore Gateway へのアクセス を拒否 24
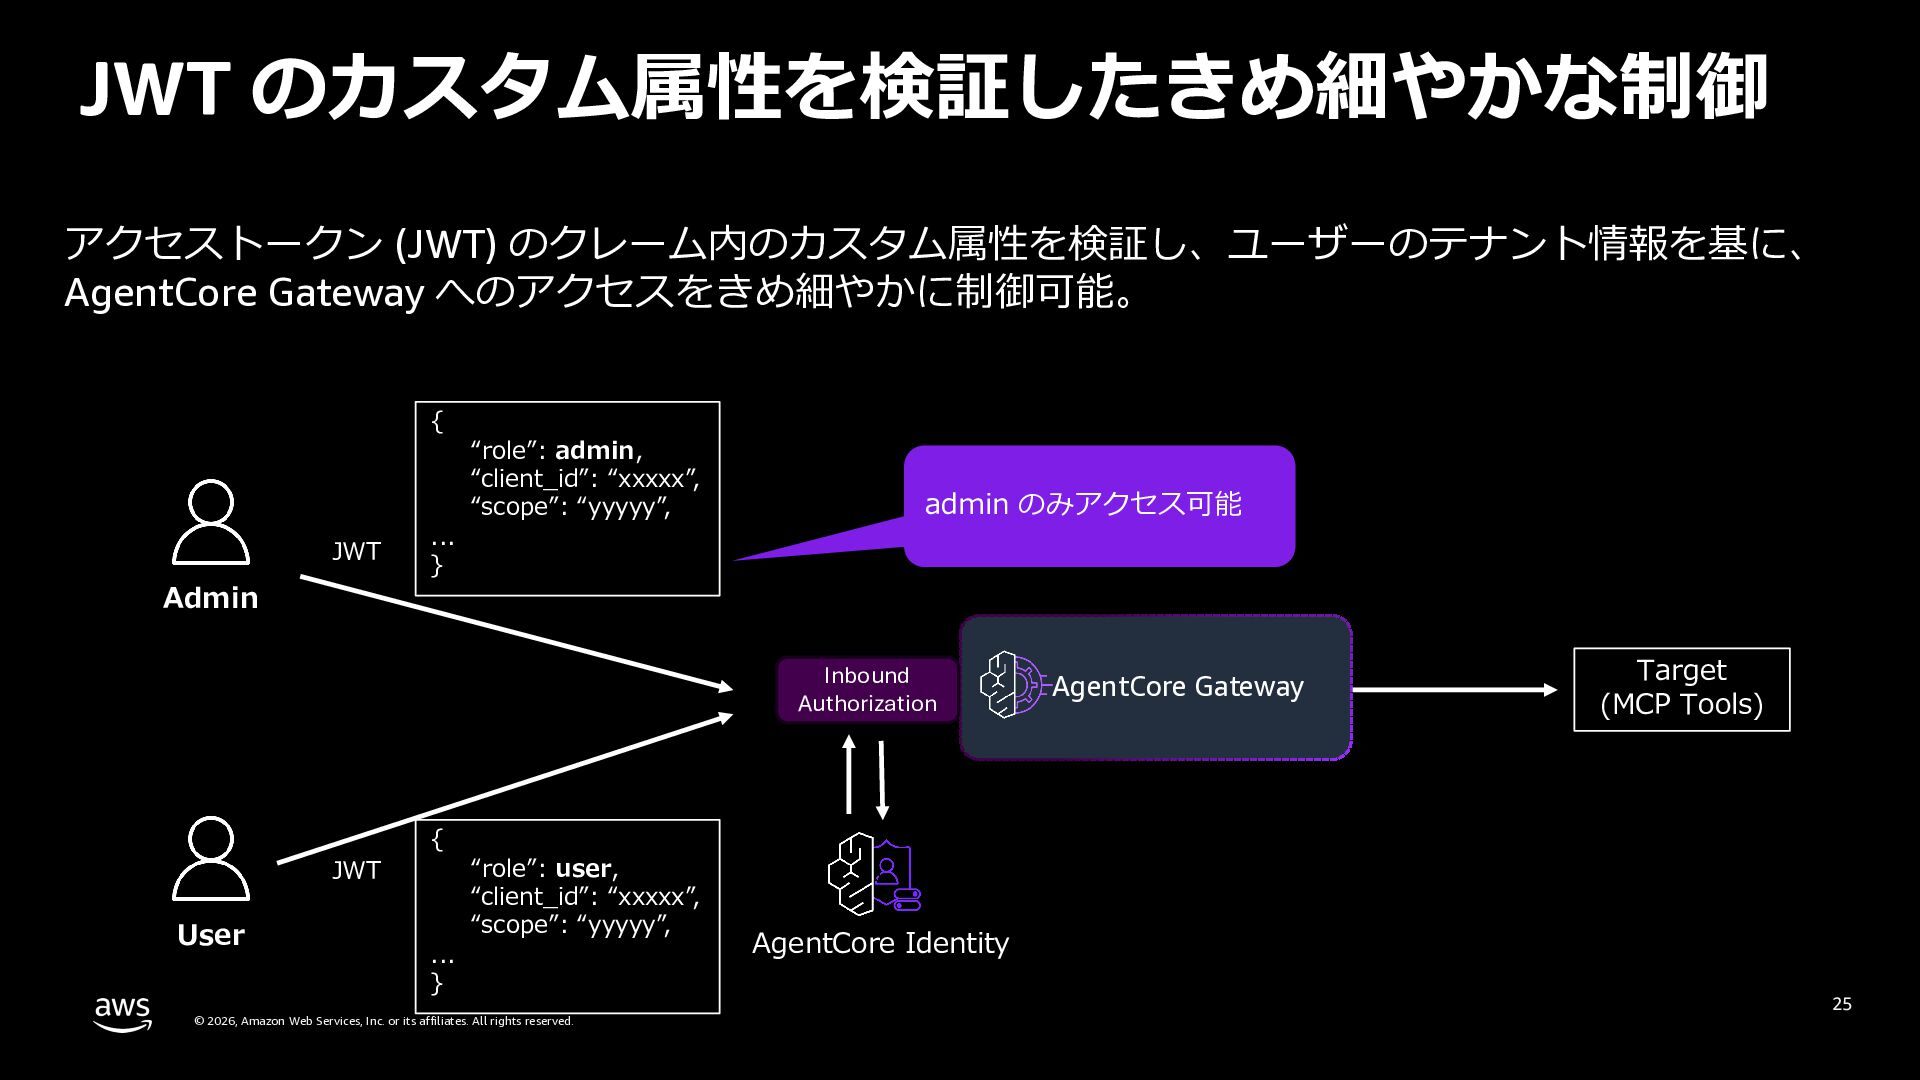
  22. JWT のカスタム属性を検証したきめ細やかな制御 アクセストークン (JWT) のクレーム内のカスタム属性を検証し、ユーザーのテナント情報を基に、 AgentCore Gateway へのアクセスをきめ細やかに制御可能。 { JWT

    Admin ... } “role”: admin, “client_id”: “xxxxx”, “scope”: “yyyyy”, admin のみアクセス可能 Inbound Authorization JWT User { ... } “role”: user, “client_id”: “xxxxx”, “scope”: “yyyyy”, © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AgentCore Gateway Target (MCP Tools) AgentCore Identity 25
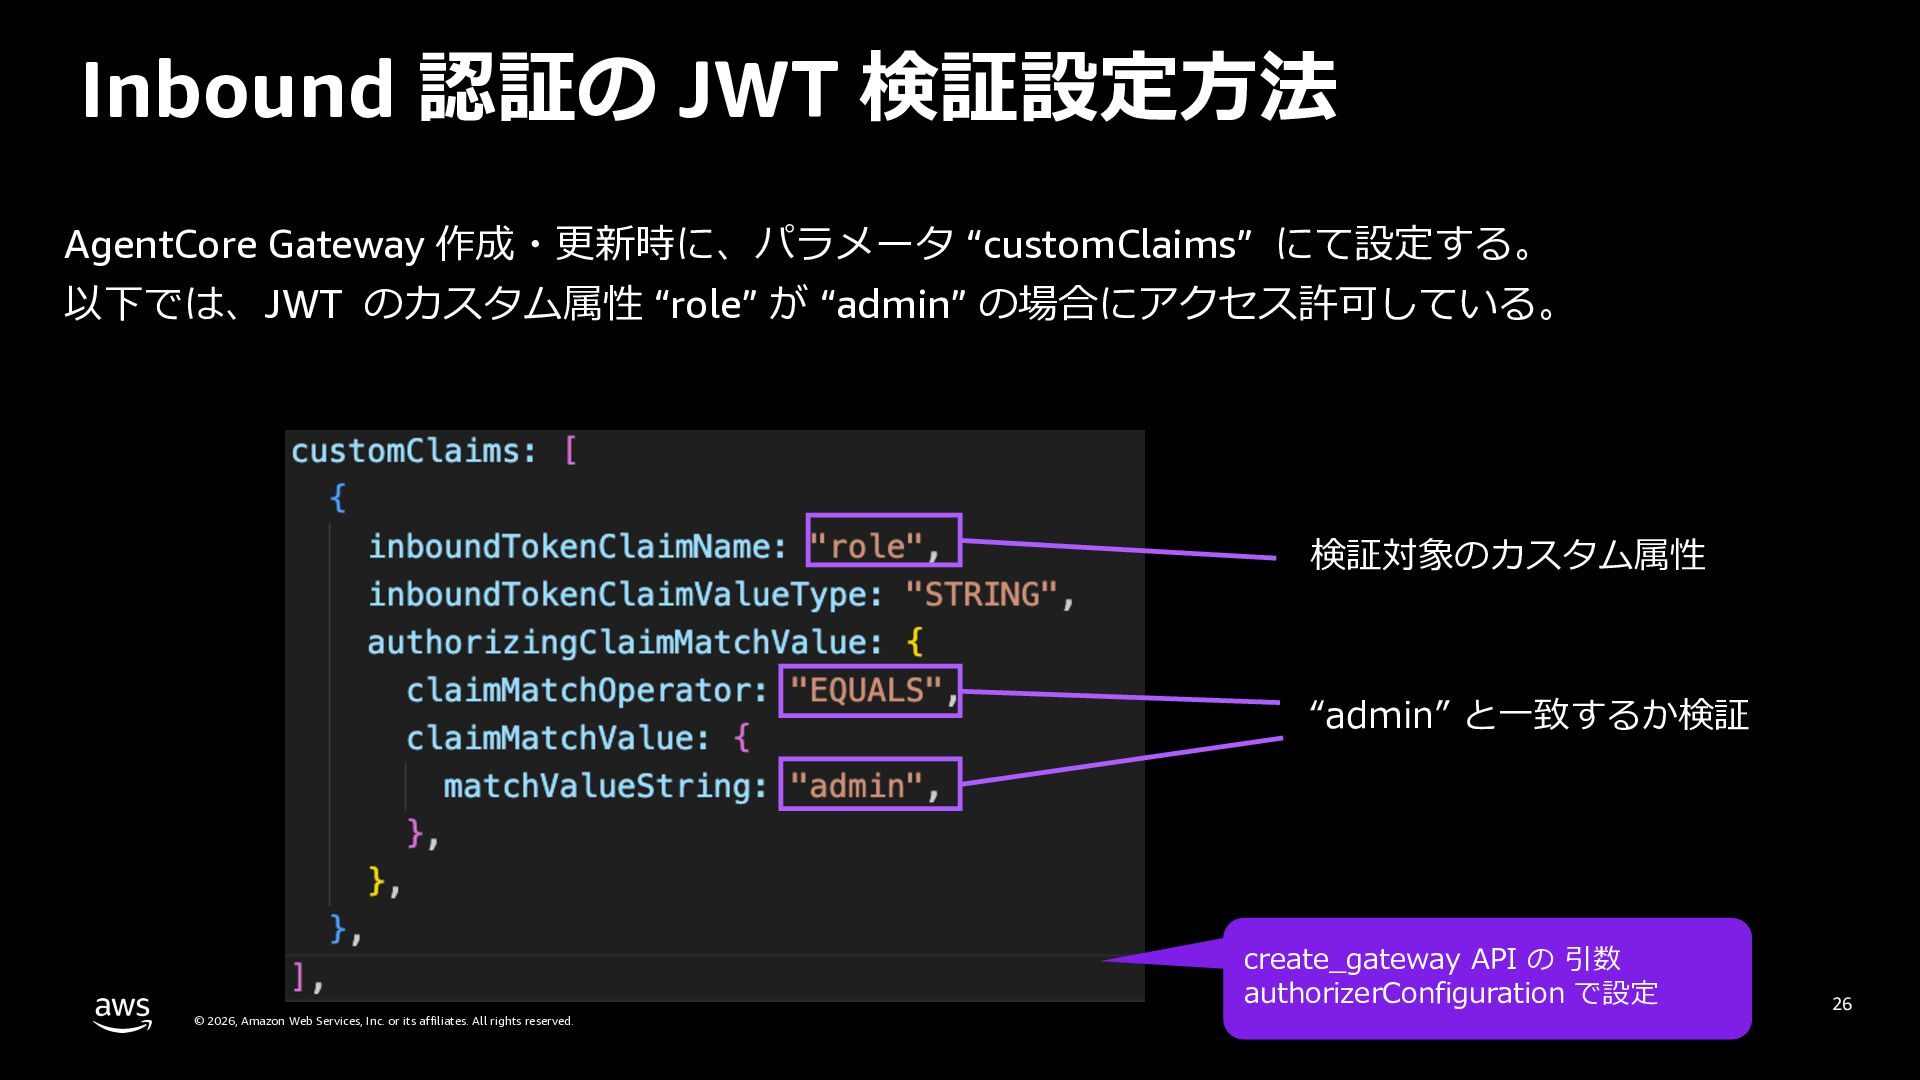
  23. Inbound 認証の JWT 検証設定⽅法 AgentCore Gateway 作成・更新時に、パラメータ “customClaims” にて設定する。 以下では、JWT

    のカスタム属性 “role” が “admin” の場合にアクセス許可している。 検証対象のカスタム属性 “admin” と⼀致するか検証 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. create_gateway / update_gateway API の 引数 authorizerConfiguration で設定 26
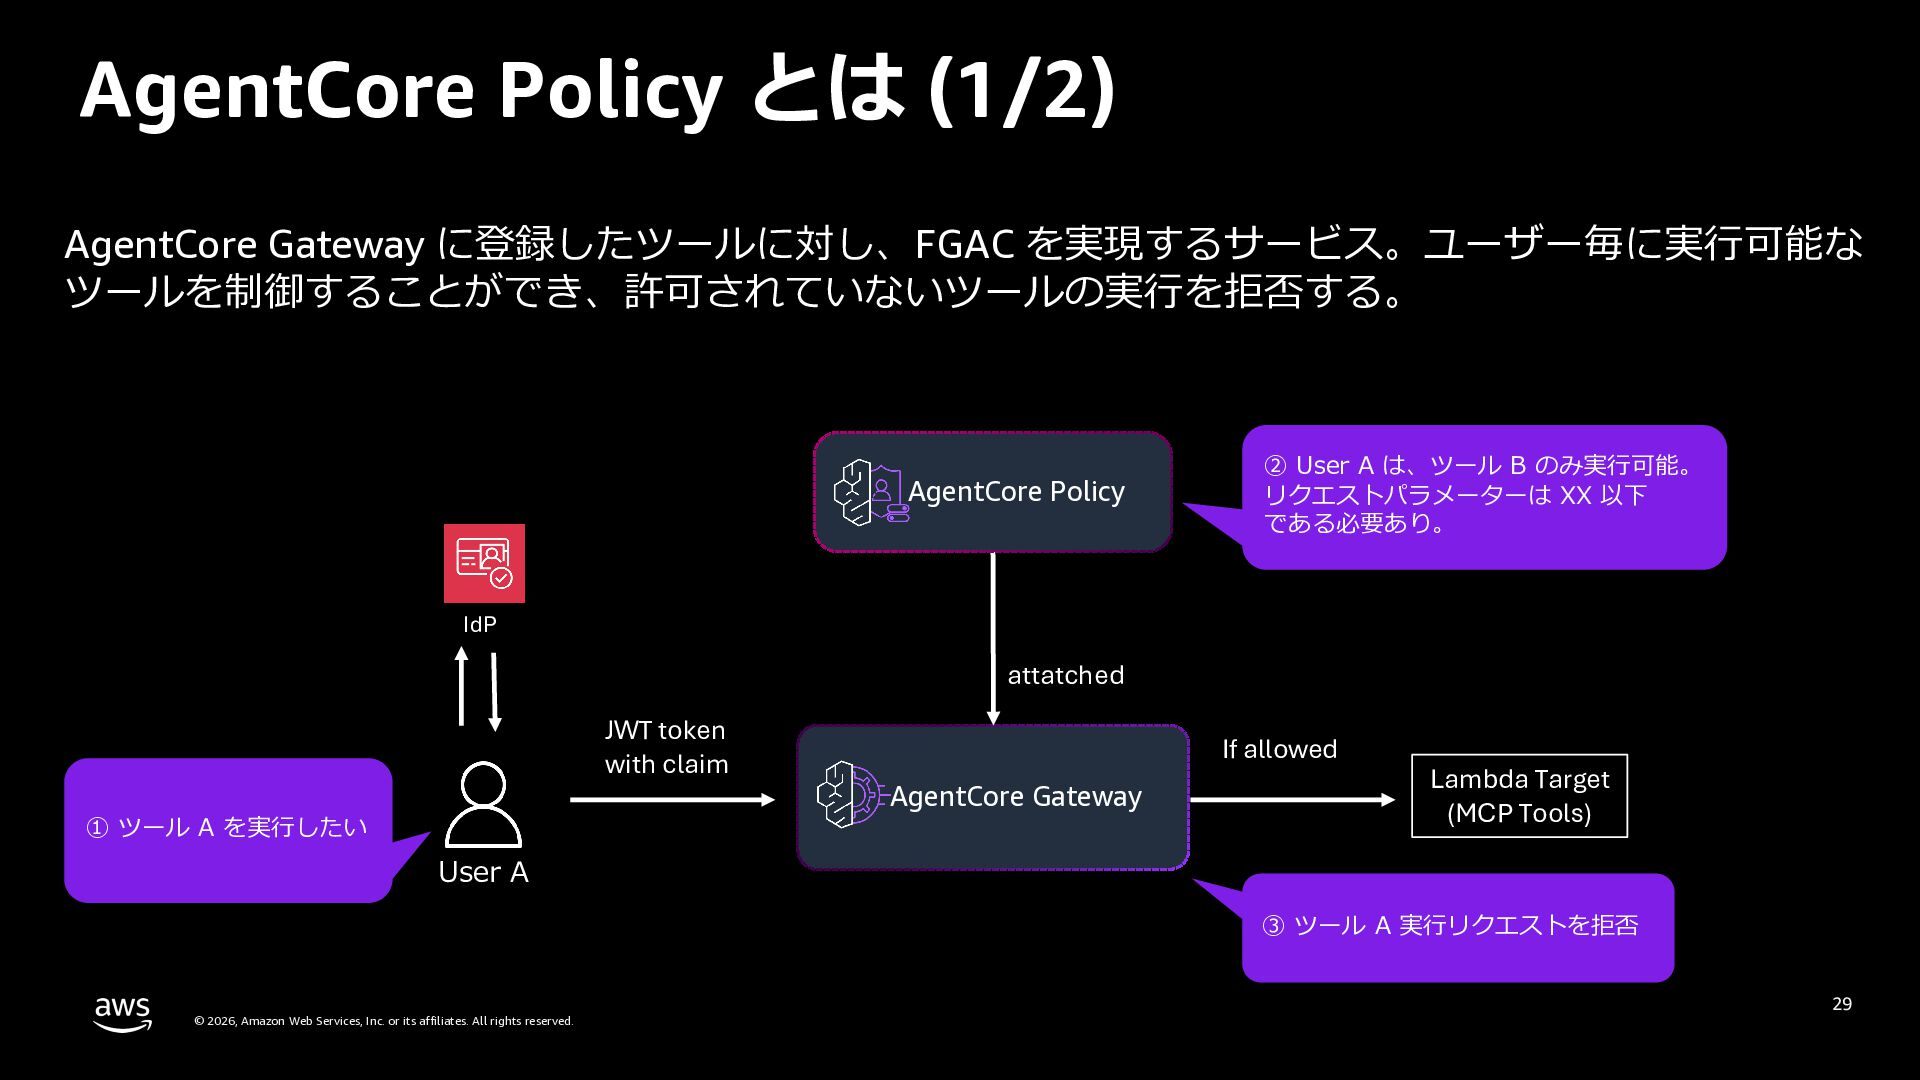
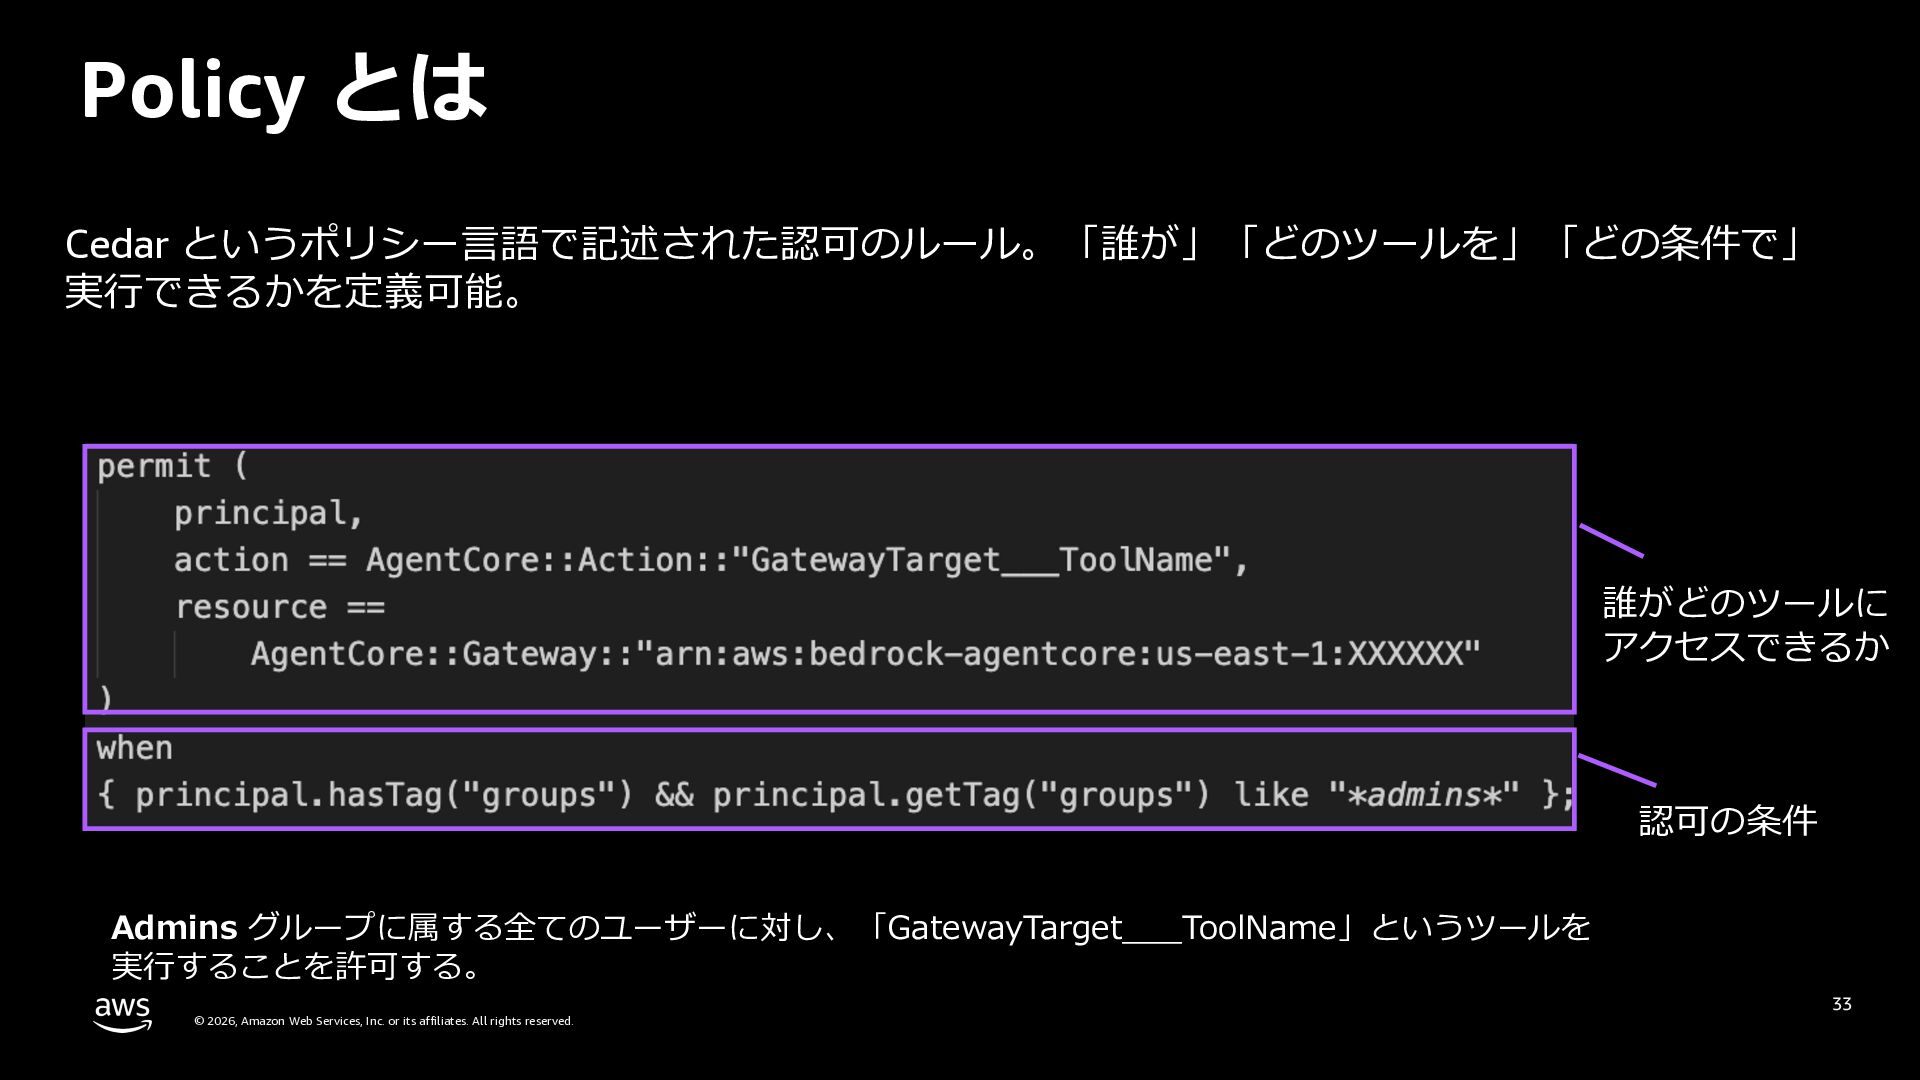
  24. AgentCore Policy とは (1/2) AgentCore Gateway に登録したツールに対し、FGAC を実現するサービス。ユーザー毎に実⾏可能な ツールを制御することができ、許可されていないツールの実⾏を拒否する。 AgentCore

    Policy ② User A は、ツール B のみ実⾏可能。 リクエストパラメーターは XX 以下 である必要あり。 IdP attatched JWT token with claim ① ツール A を実⾏したい If allowed AgentCore Gateway Lambda Target (MCP Tools) User A ③ ツール A 実⾏リクエストを拒否 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 29
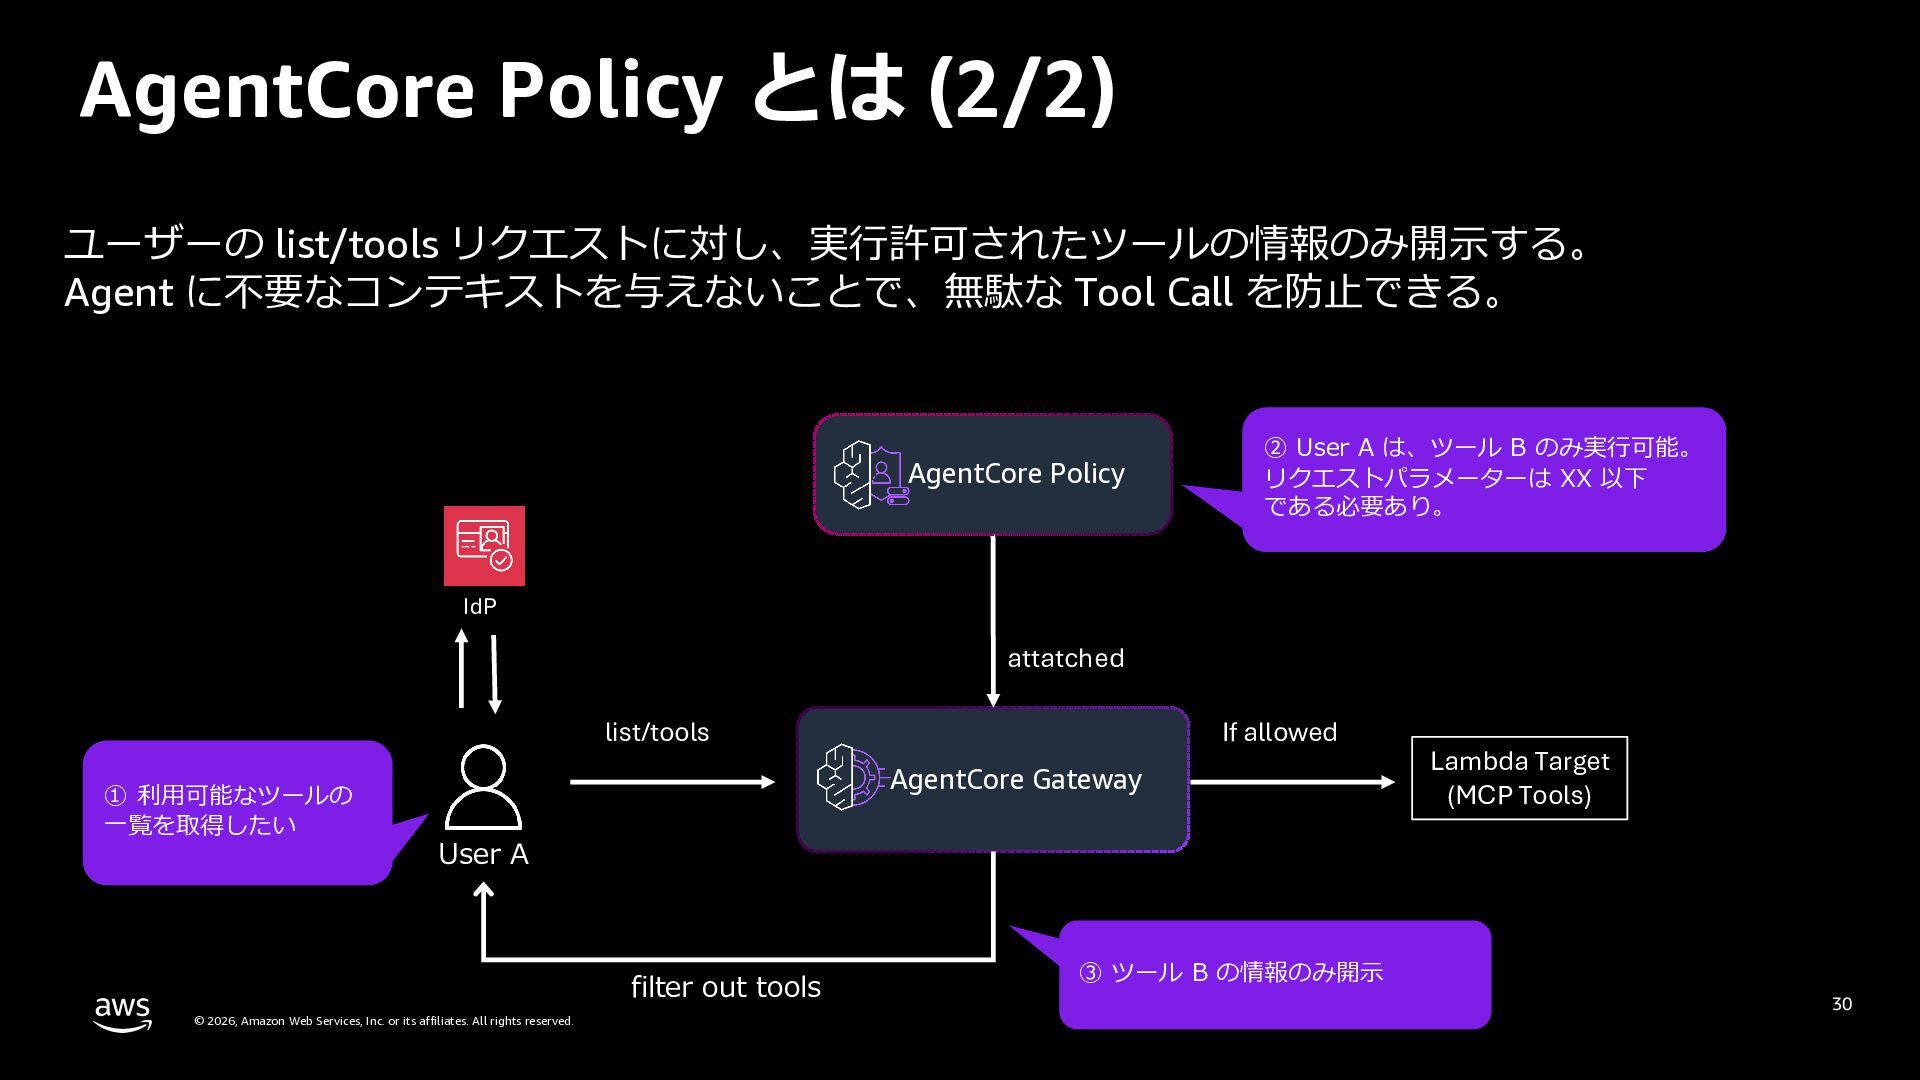
  25. AgentCore Policy とは (2/2) ユーザーの list/tools リクエストに対し、実⾏許可されたツールの情報のみ開⽰する。 Agent に不要なコンテキストを与えないことで、無駄な Tool

    Call を防⽌できる。 AgentCore Policy ② User A は、ツール B のみ実⾏可能。 リクエストパラメーターは XX 以下 である必要あり。 IdP attatched list/tools ① 利⽤可能なツールの ⼀覧を取得したい If allowed AgentCore Gateway Lambda Target (MCP Tools) User A filter out tools © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ③ ツール B の情報のみ開⽰ 30
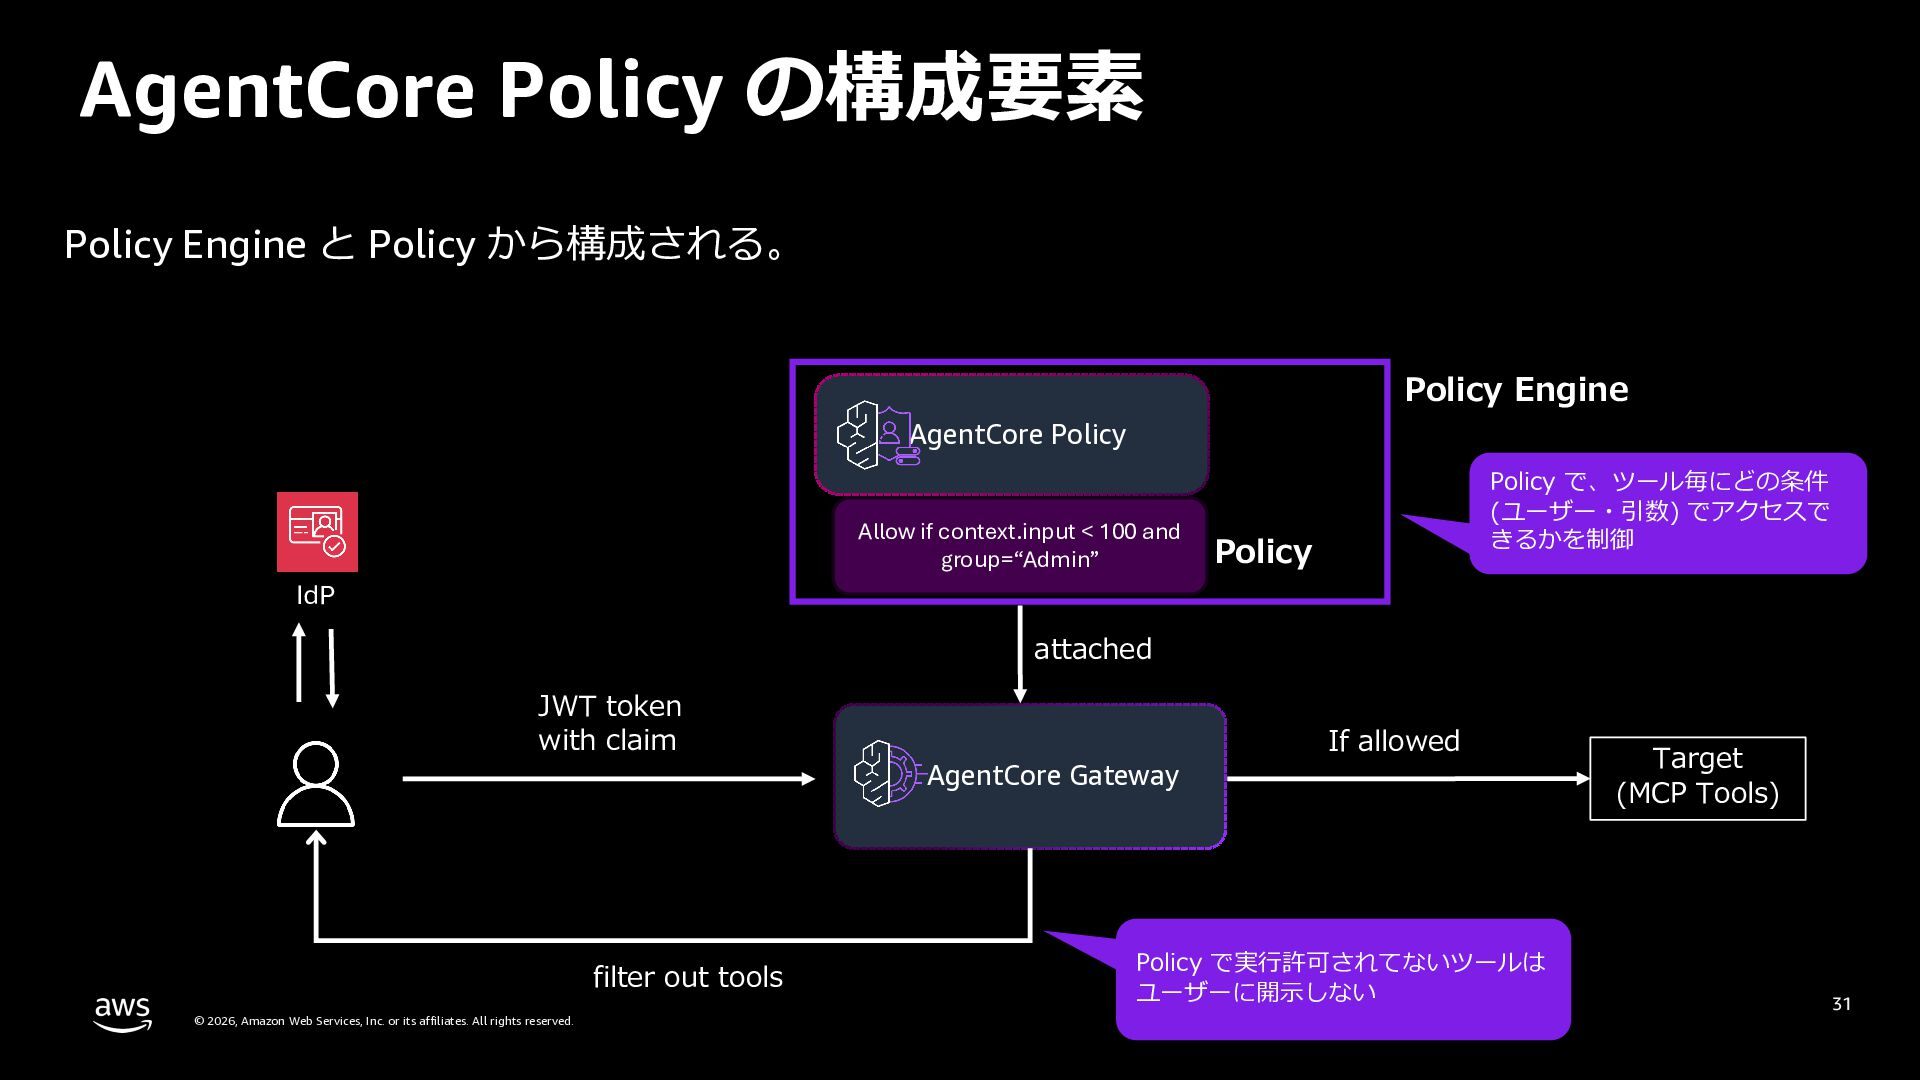
  26. AgentCore Policy の構成要素 Policy Engine と Policy から構成される。 Policy Engine

    AgentCore Policy Allow if context.input < 100 and group=“Admin” Policy で、ツール毎にどの条件 (ユーザー・引数) でアクセスで きるかを制御 Policy IdP attached JWT token with claim filter out tools © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AgentCore Gateway If allowed Policy で実⾏許可されてないツールは ユーザーに開⽰しない Target (MCP Tools) 31
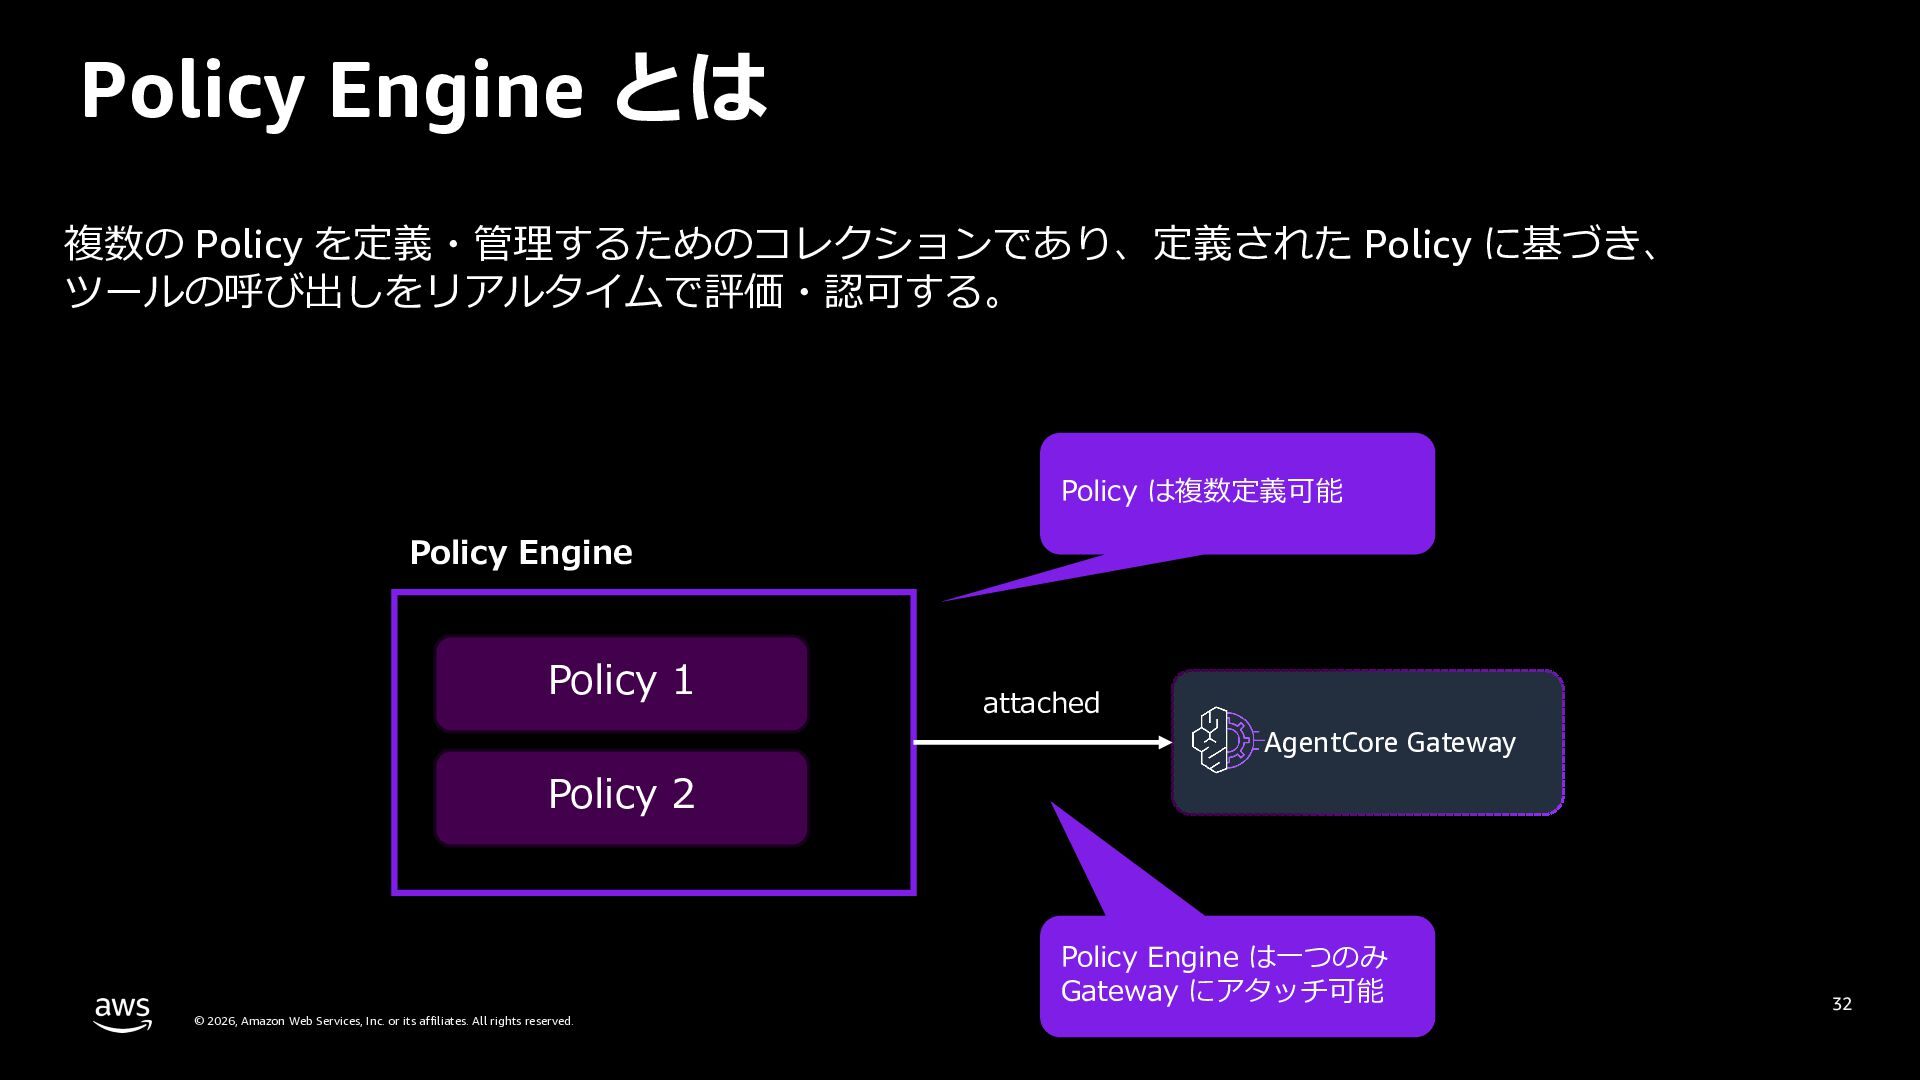
  27. Policy Engine とは 複数の Policy を定義・管理するためのコレクションであり、定義された Policy に基づき、 ツールの呼び出しをリアルタイムで評価・認可する。 Policy

    は複数定義可能 Policy Engine Policy 1 attached AgentCore Gateway Policy 2 Policy Engine は⼀つのみ Gateway にアタッチ可能 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 32
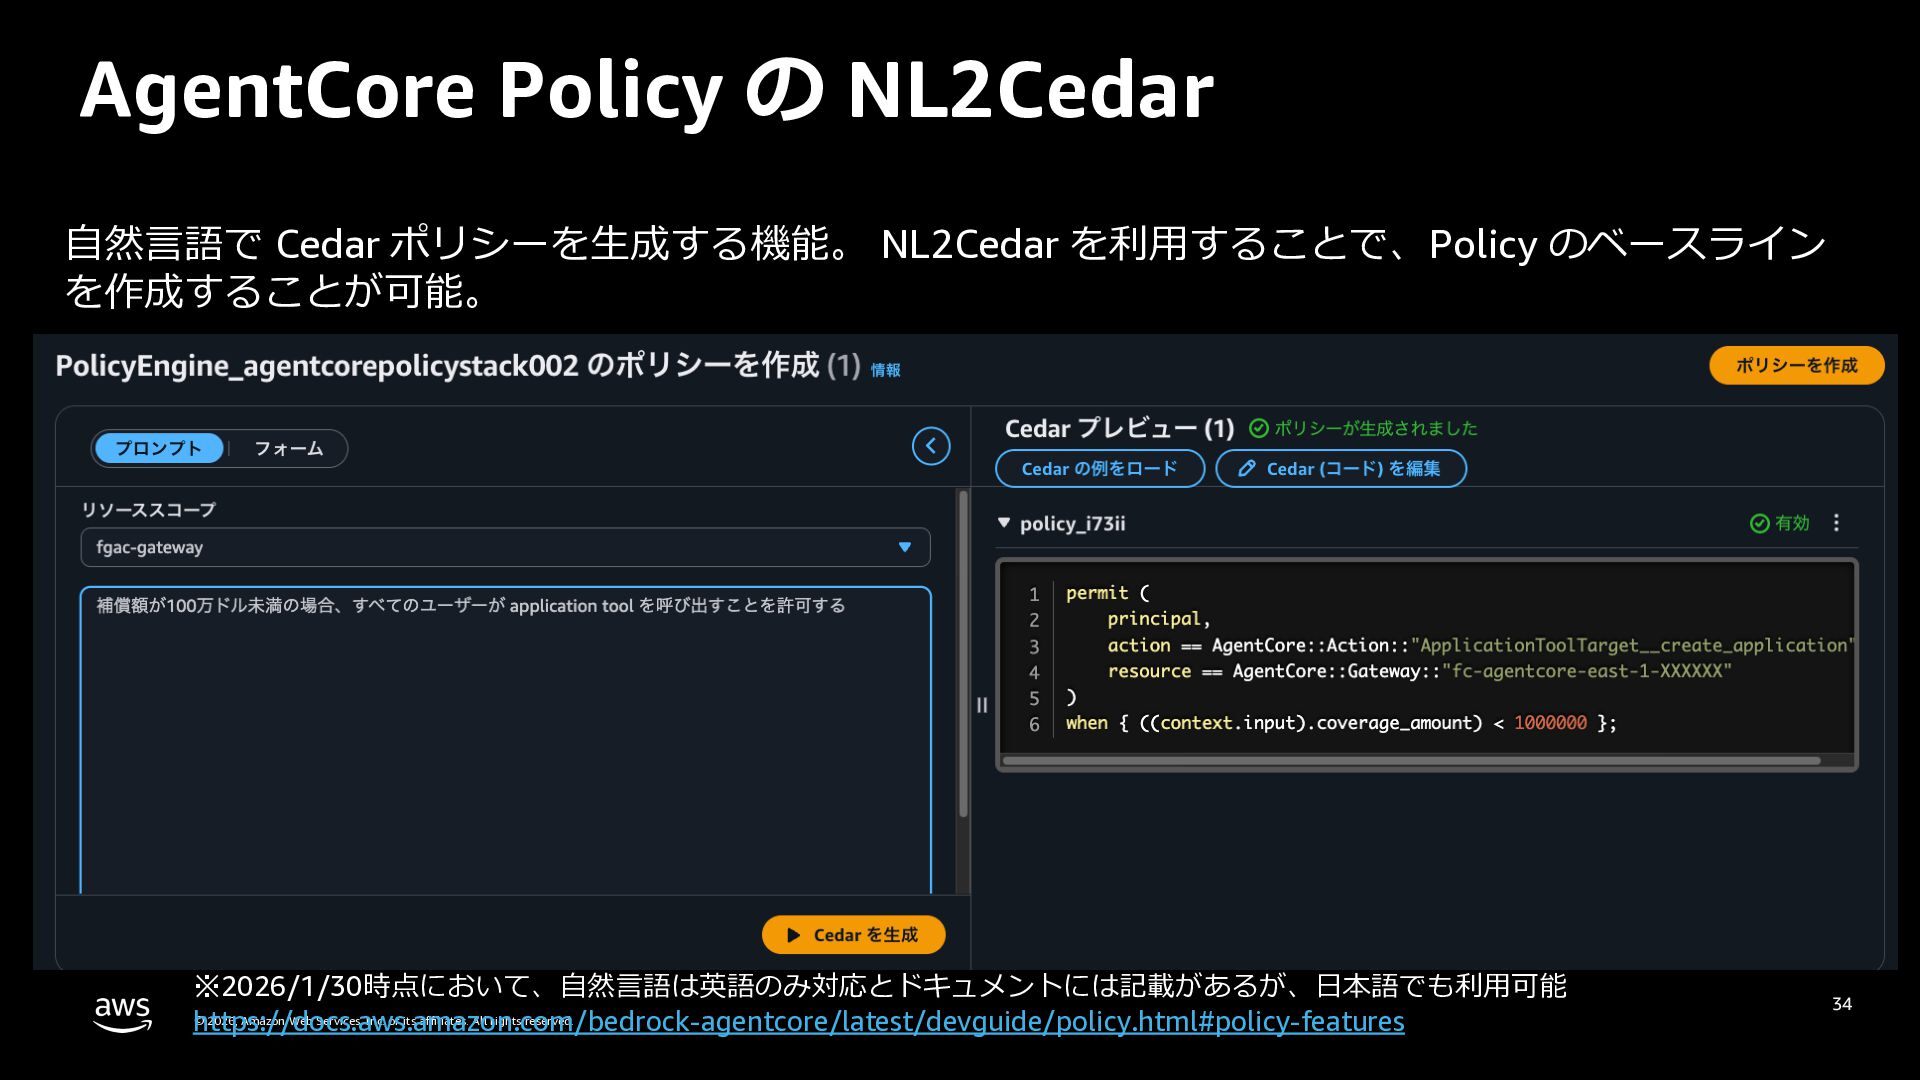
  28. AgentCore Policy の NL2Cedar ⾃然⾔語で Cedar ポリシーを⽣成する機能。 NL2Cedar を利⽤することで、Policy のベースライン

    を作成することが可能。 ※2026/6/12時点において、⾃然⾔語は英語のプロンプトで⽣成可能とドキュメントには記載があるが、⽇本語でも利⽤可能 https://docs.aws.amazon.com/bedrock-agentcore/latest/devguide/policy.html#policy-features © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 34
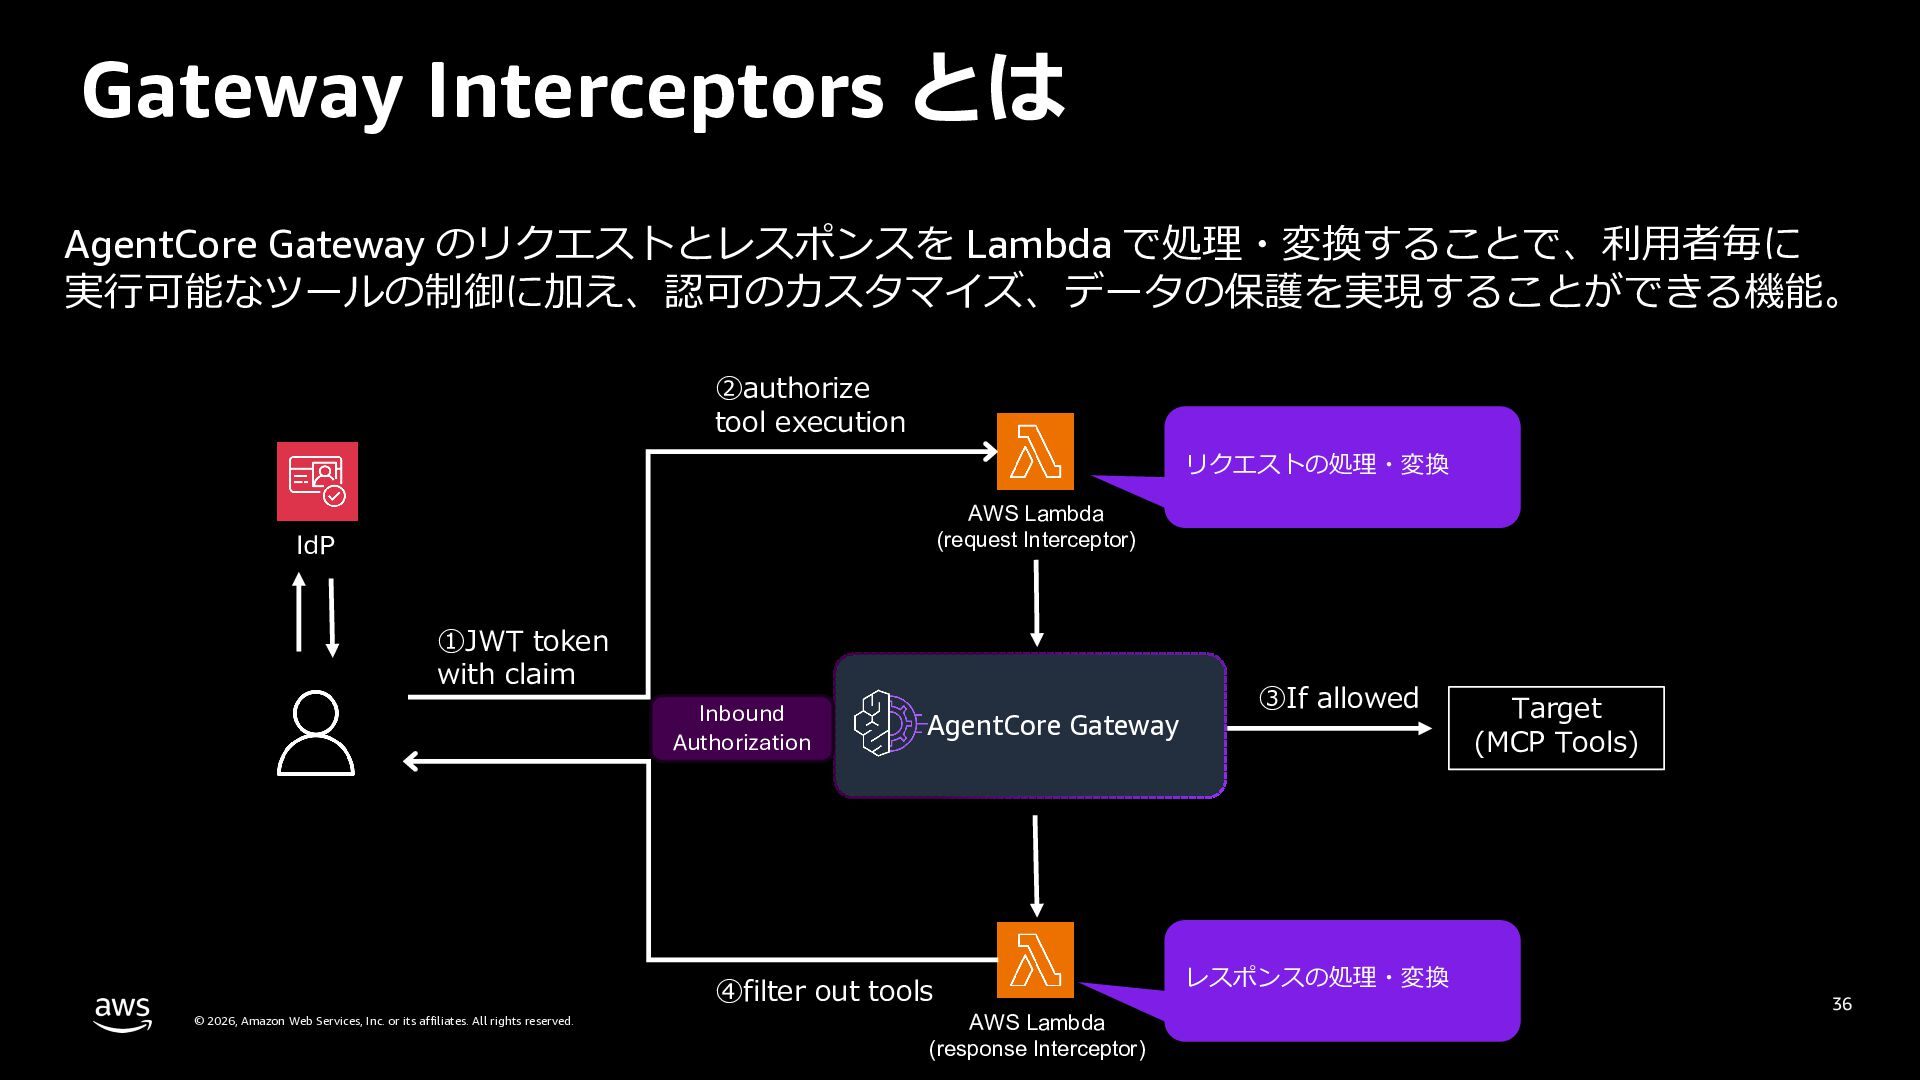
  29. Gateway Interceptors とは AgentCore Gateway のリクエストとレスポンスを Lambda で処理・変換することで、利⽤者毎に 実⾏可能なツールの制御に加え、認可のカスタマイズ、データの保護を実現することができる機能。 ②authorize

    tool execution リクエストの処理・変換 AWS Lambda (request Interceptor) IdP ①JWT token with claim Inbound Authorization AgentCore Gateway ④filter out tools © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AWS Lambda (response Interceptor) ③If allowed レスポンスの処理・変換 Target (MCP Tools) 36
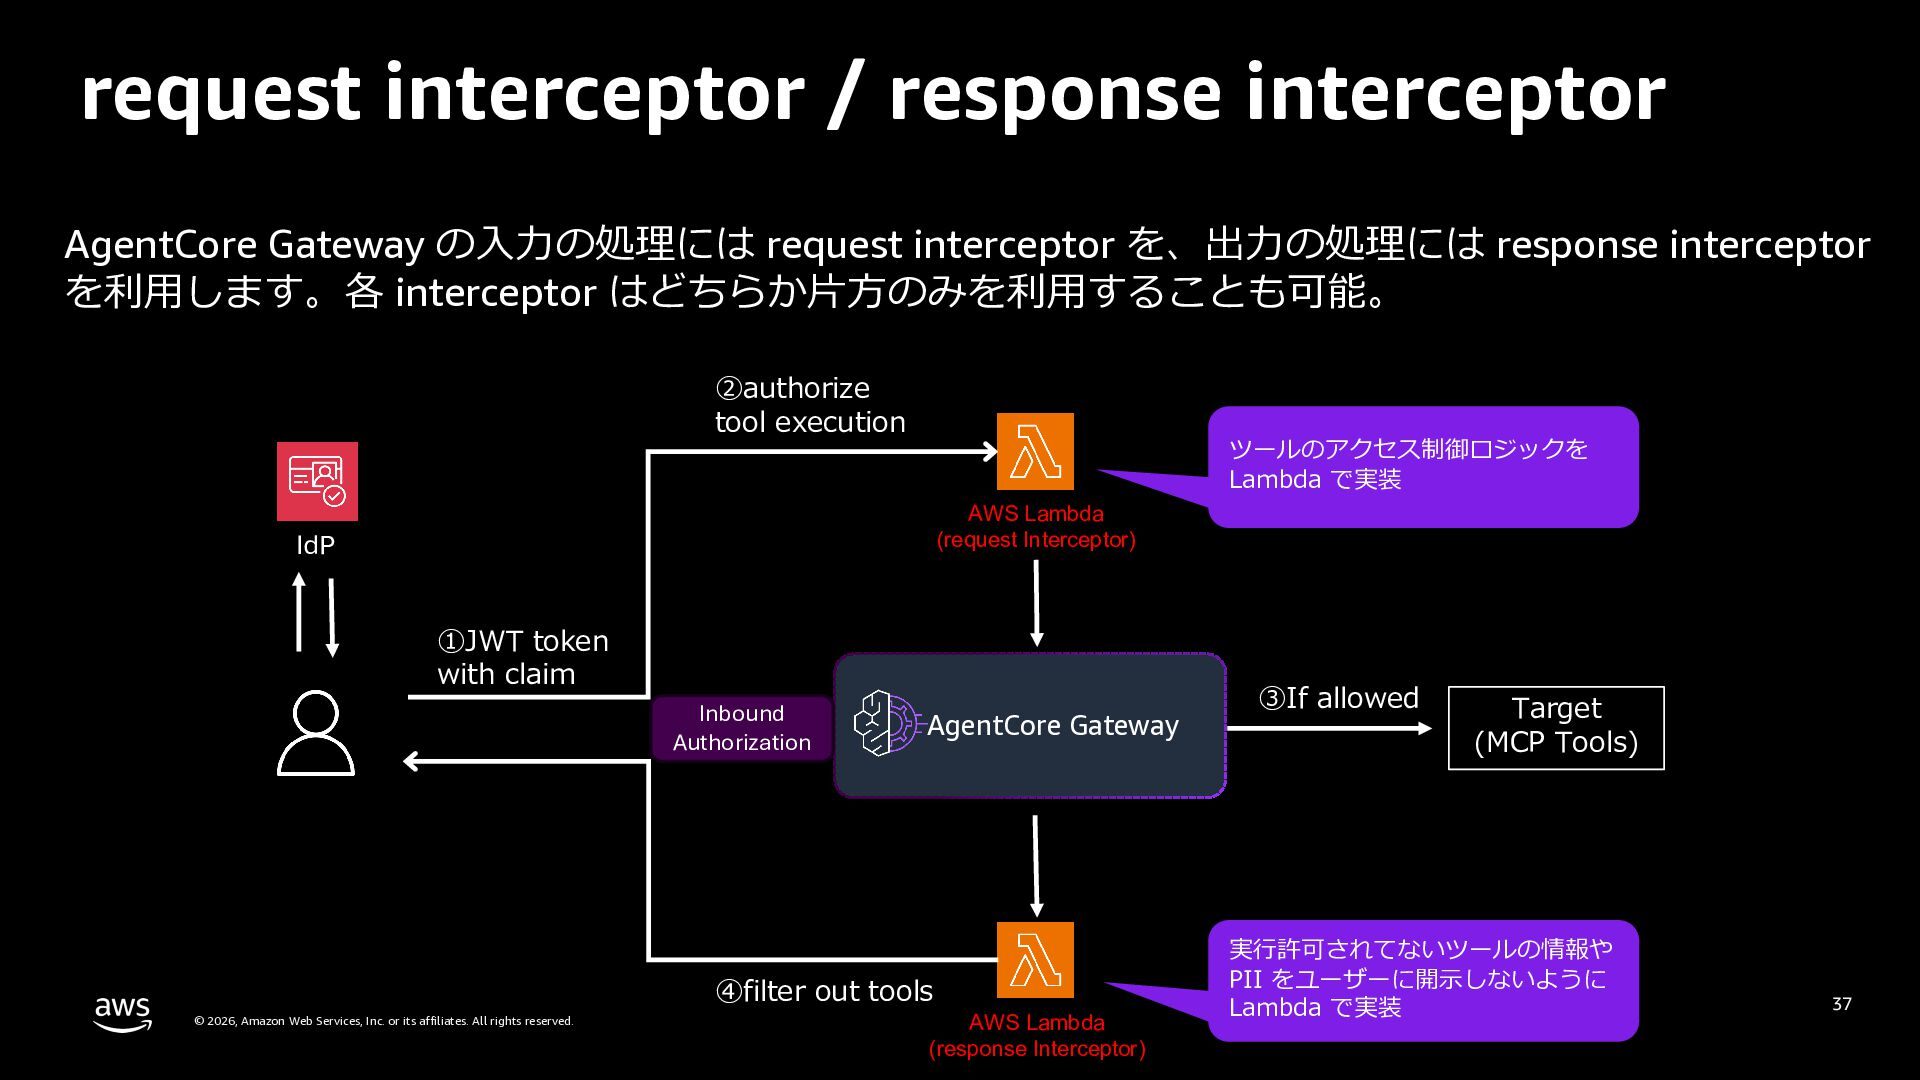
  30. request interceptor / response interceptor AgentCore Gateway の⼊⼒の処理には request interceptor

    を、出⼒の処理には response interceptor を利⽤します。各 interceptor はどちらか⽚⽅のみを利⽤することも可能。 ②authorize tool execution ツールのアクセス制御ロジックを Lambda で実装 AWS Lambda (request Interceptor) IdP ①JWT token with claim Inbound Authorization AgentCore Gateway ④filter out tools © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AWS Lambda (response Interceptor) ③If allowed Target (MCP Tools) 実⾏許可されてないツールの情報や PII をユーザーに開⽰しないように Lambda で実装 37
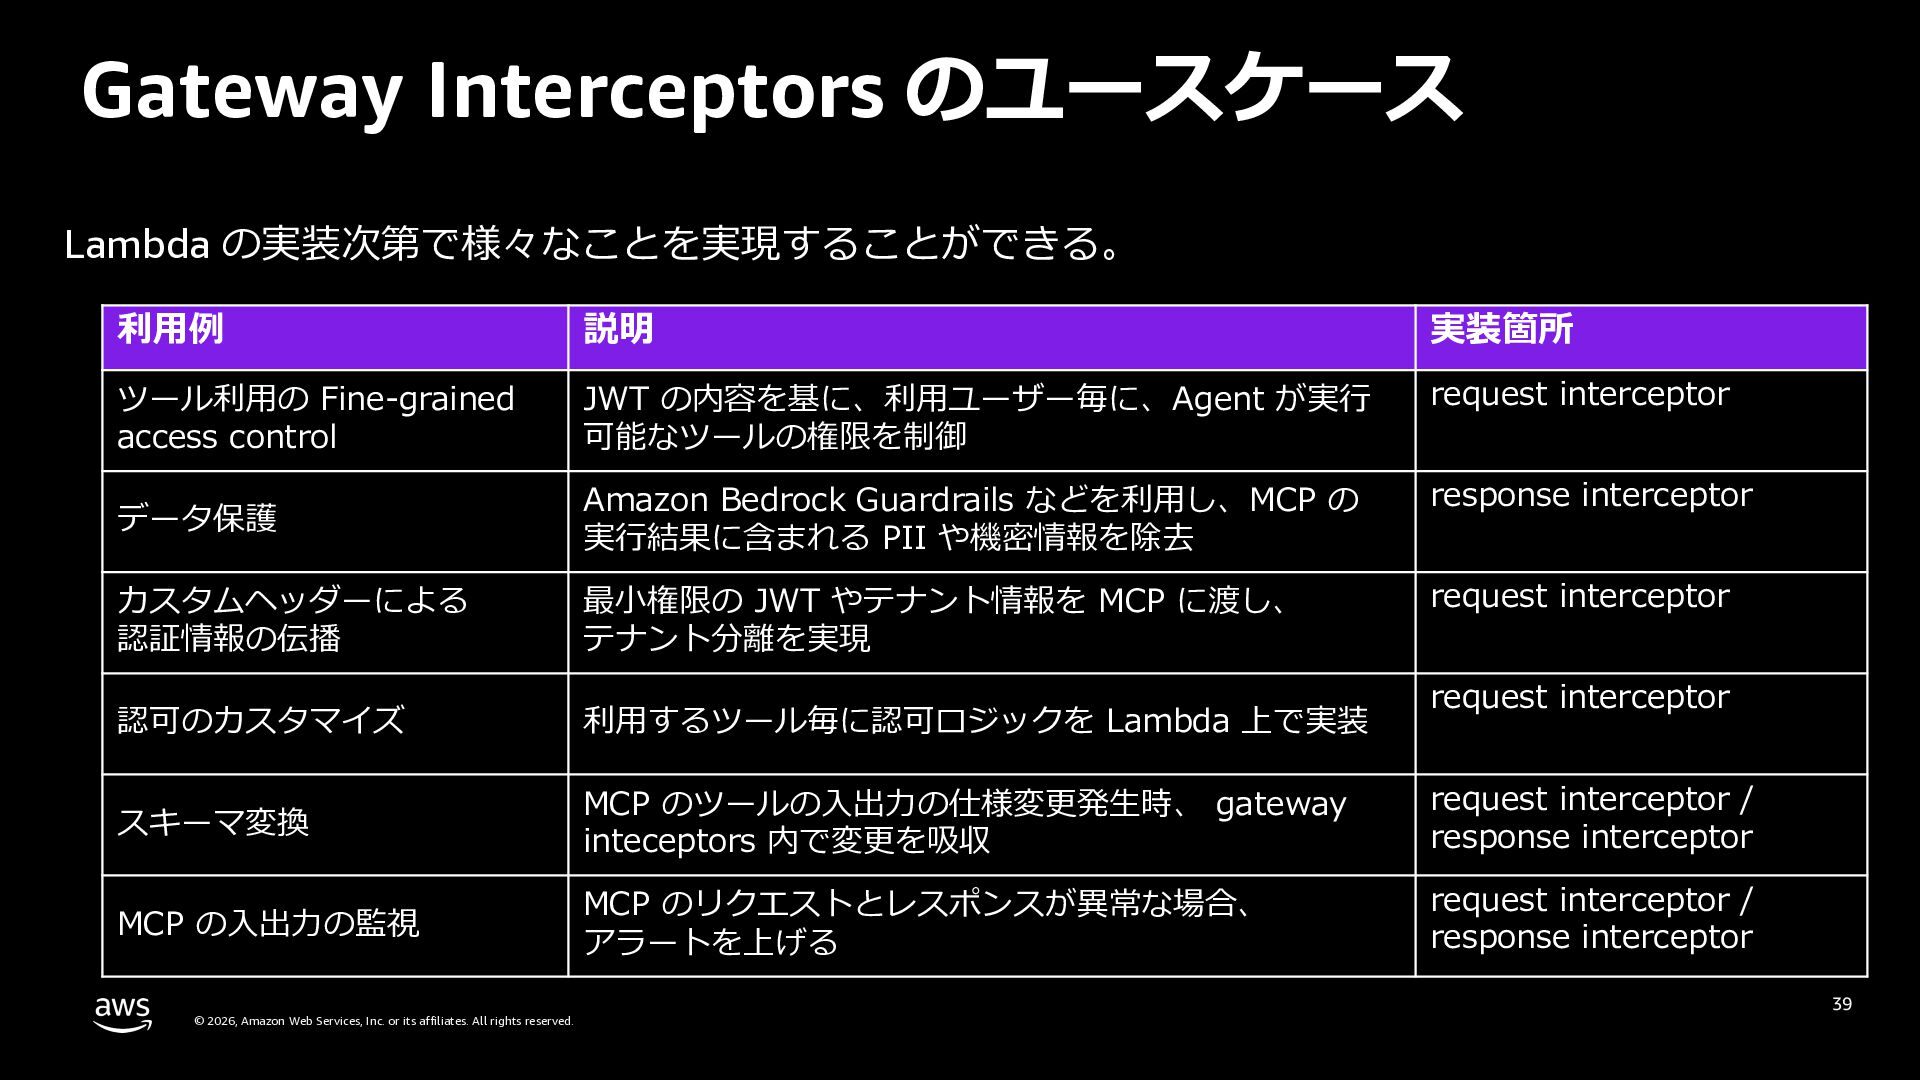
  31. Gateway Interceptors のユースケース Lambda の実装次第で様々なことを実現することができる。 利⽤例 説明 実装箇所 ツール利⽤の Fine-grained

    access control JWT の内容を基に、利⽤ユーザー毎に、Agent が実⾏ 可能なツールの権限を制御 request interceptor データ保護 Amazon Bedrock Guardrails などを利⽤し、MCP の 実⾏結果に含まれる PII や機密情報を除去 response interceptor カスタムヘッダーによる 認証情報の伝播 最⼩権限の JWT やテナント情報を MCP に渡し、 テナント分離を実現 request interceptor 認可のカスタマイズ 利⽤するツール毎に認可ロジックを Lambda 上で実装 スキーマ変換 MCP のツールの⼊出⼒の仕様変更発⽣時、 gateway inteceptors 内で変更を吸収 request interceptor / response interceptor MCP の⼊出⼒の監視 MCP のリクエストとレスポンスが異常な場合、 アラートを上げる request interceptor / response interceptor © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. request interceptor 39
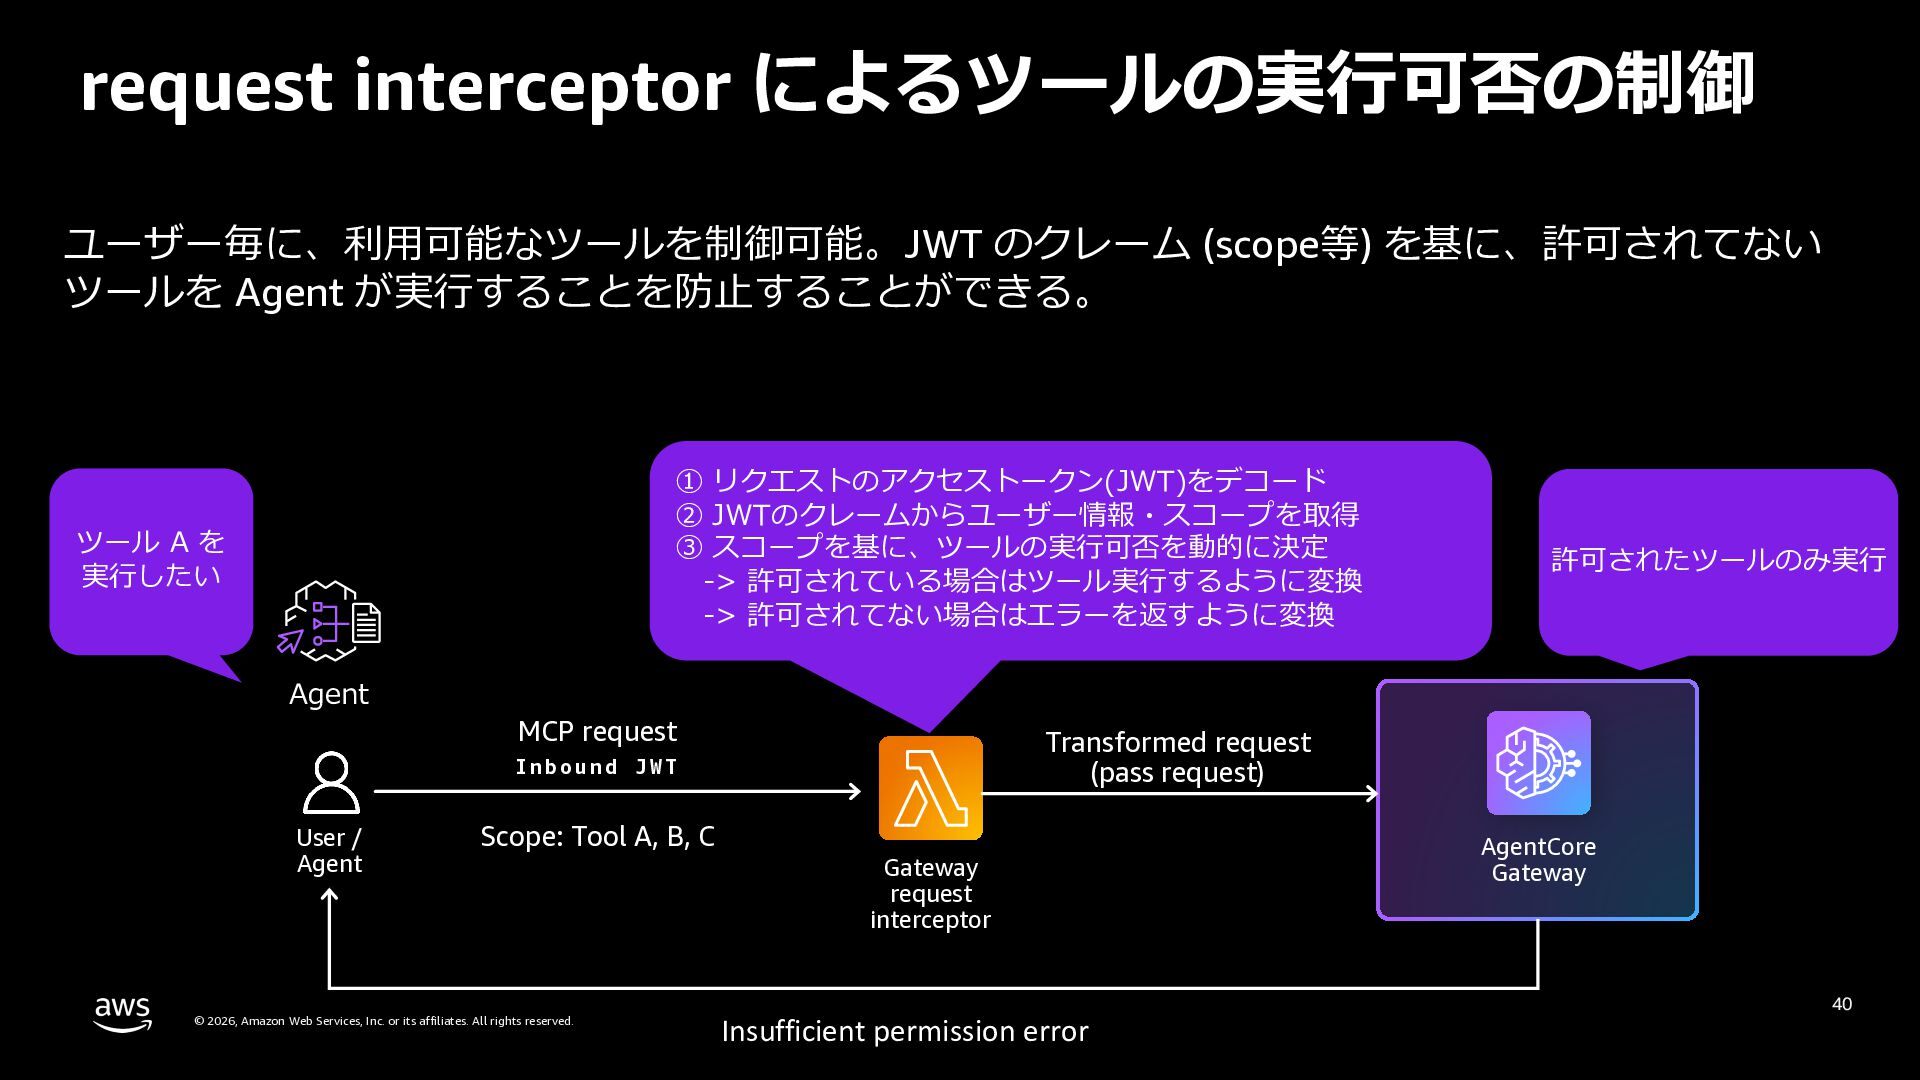
  32. request interceptor によるツールの実⾏可否の制御 ユーザー毎に、利⽤可能なツールを制御可能。JWT のクレーム (scope等) を基に、許可されてない ツールを Agent が実⾏することを防⽌することができる。

    ① リクエストのアクセストークン(JWT)をデコード ② JWTのクレームからユーザー情報・スコープを取得 ③ スコープを基に、ツールの実⾏可否を動的に決定 -> 許可されている場合はツール実⾏するように変換 -> 許可されてない場合はエラーを返すように変換 ツール A を 実⾏したい Agent MCP request Transformed request (pass request) Inbound JWT User / Agent Scope: Tool A, B, C © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 許可されたツールのみ実⾏ Gateway request interceptor Insufficient permission error AgentCore Gateway 40
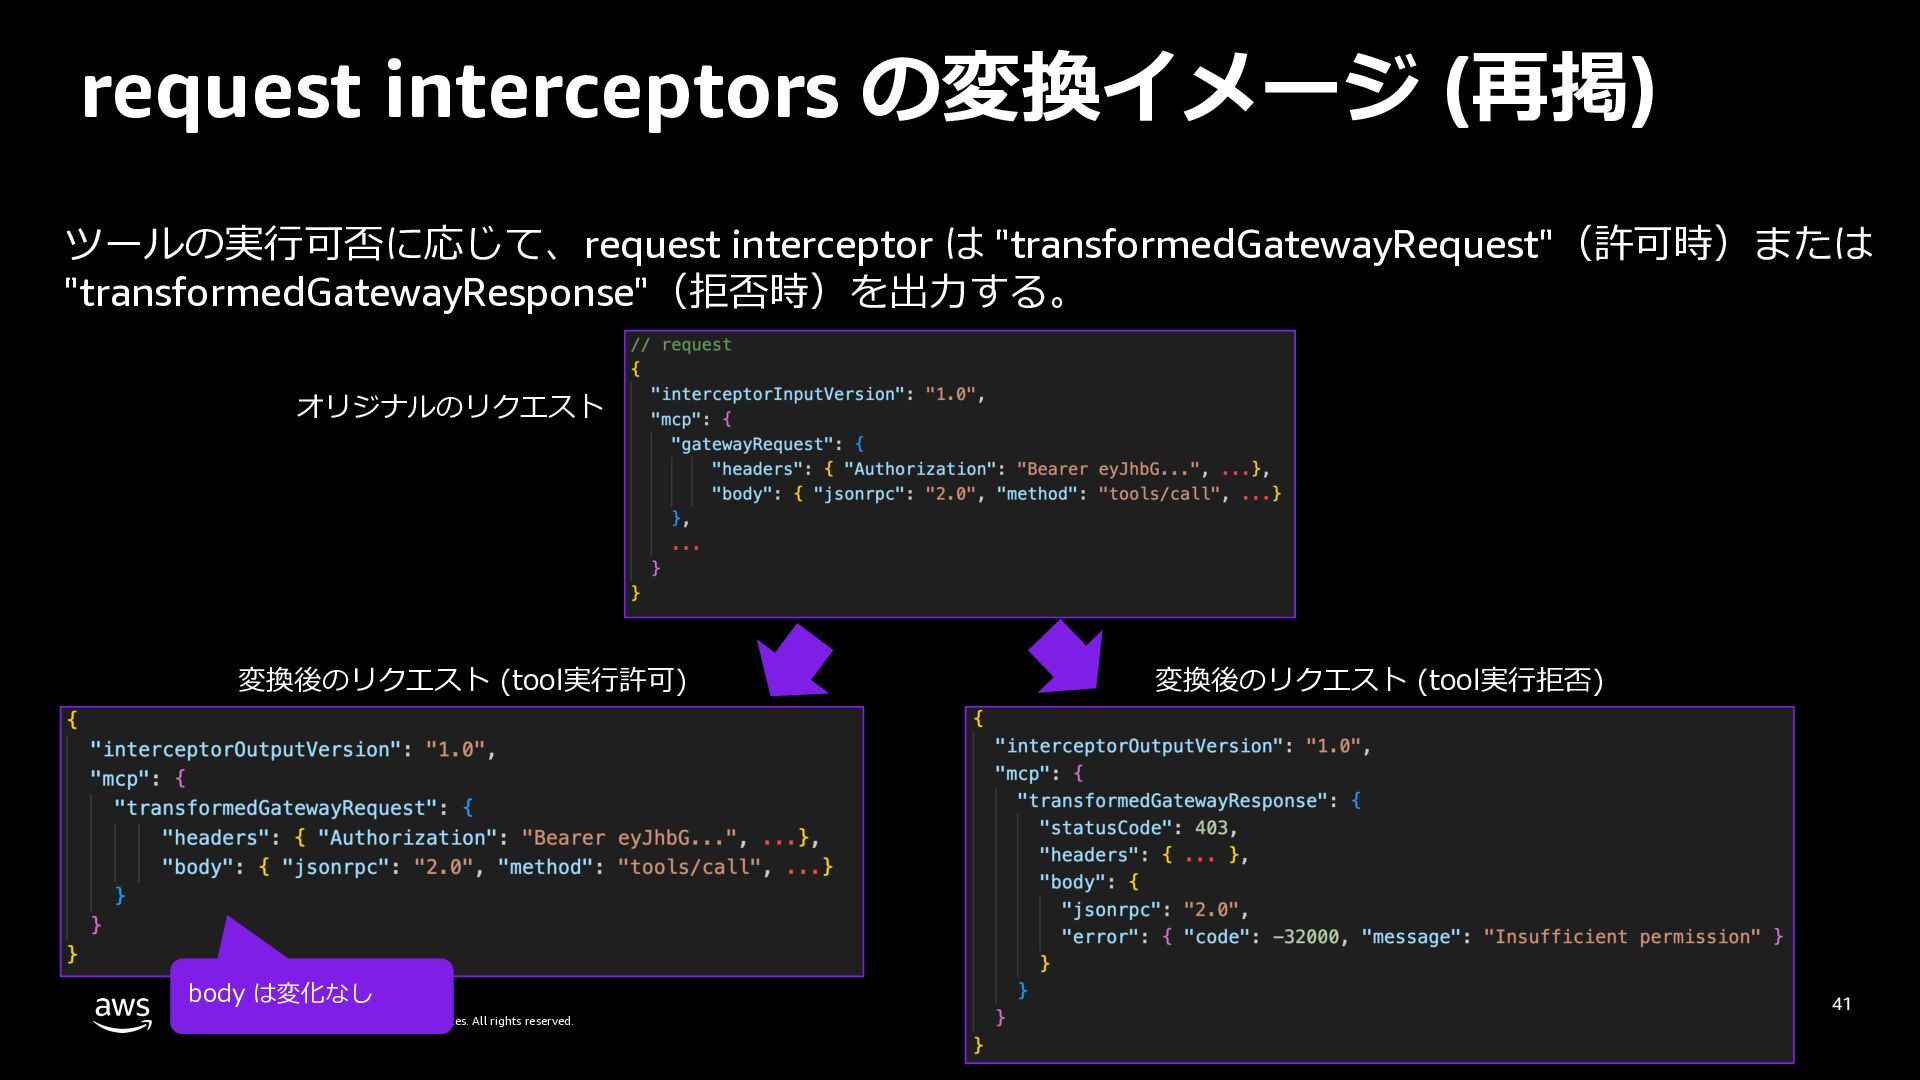
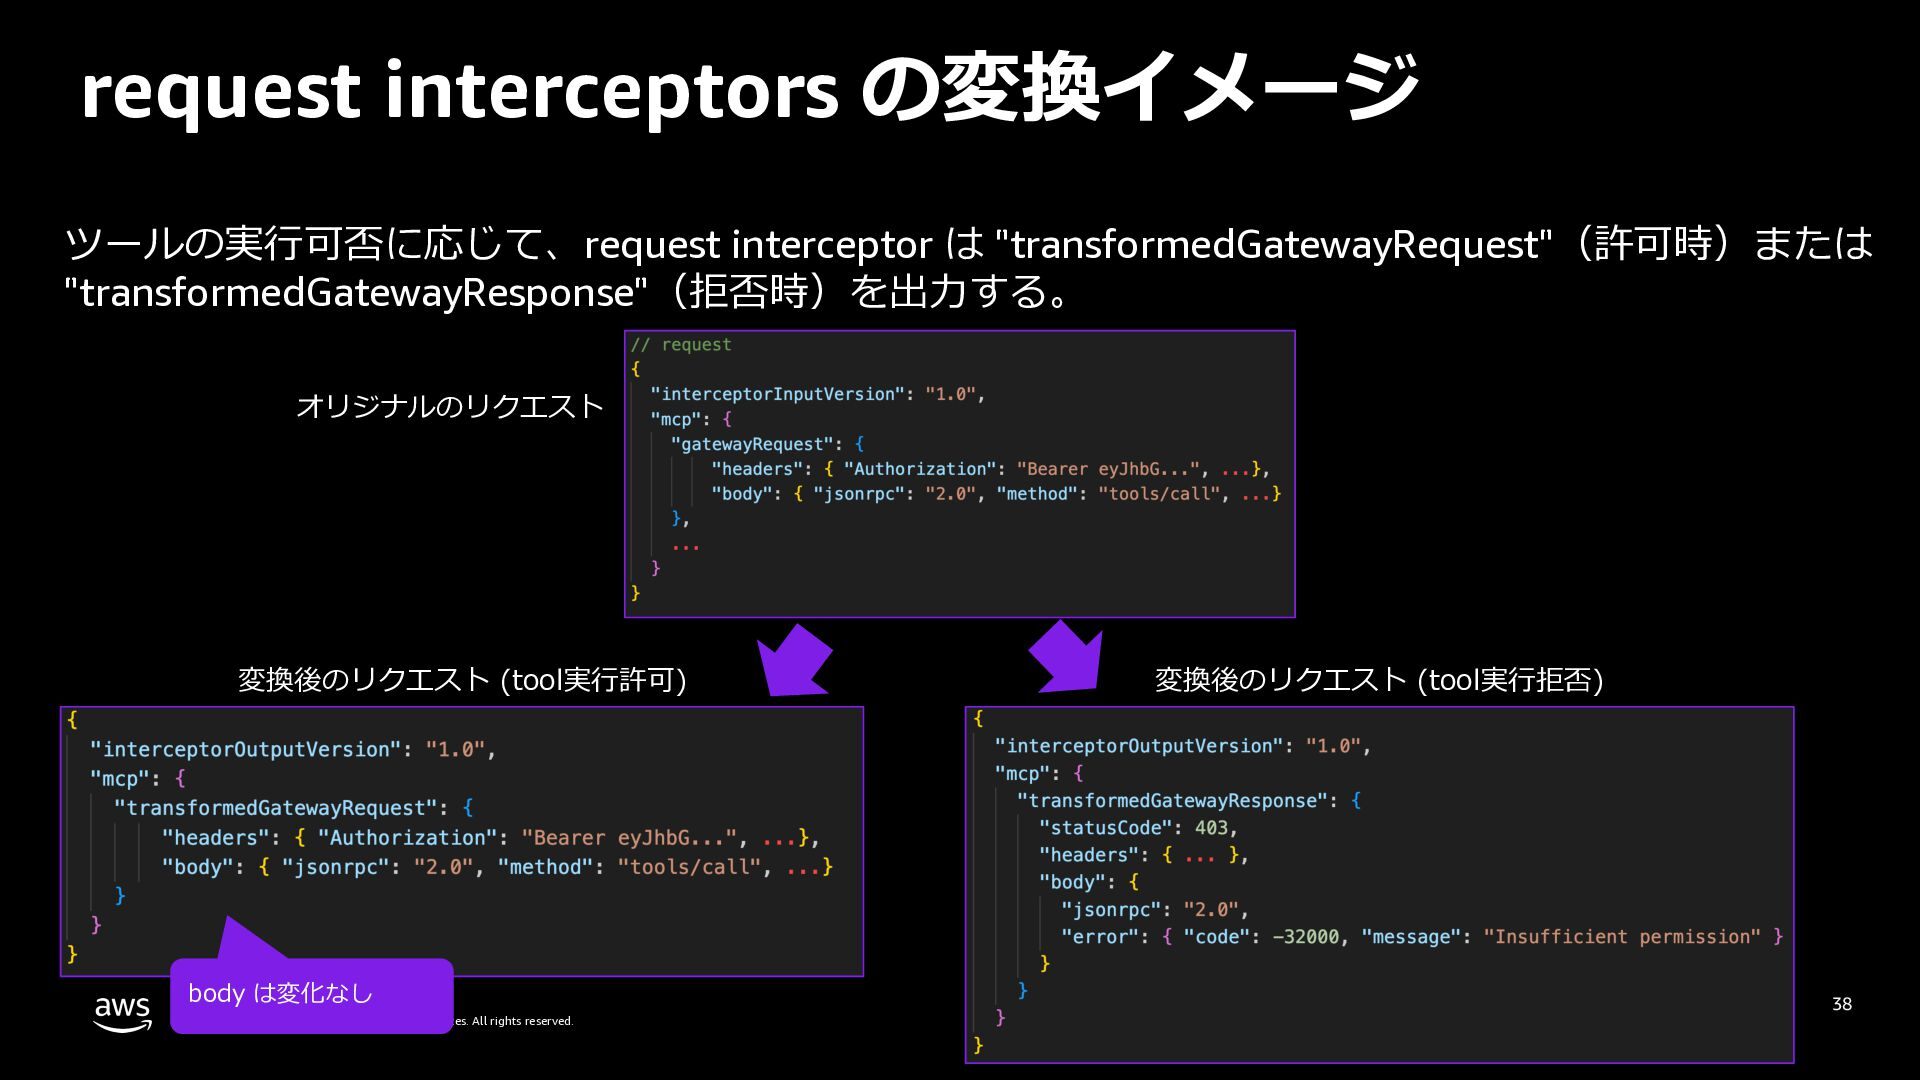
  33. request interceptors の変換イメージ (再掲) ツールの実⾏可否に応じて、request interceptor は "transformedGatewayRequest"(許可時)または "transformedGatewayResponse"(拒否時)を出⼒する。 オリジナルのリクエスト

    変換後のリクエスト (tool実⾏許可) body は変化なし © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 変換後のリクエスト (tool実⾏拒否) 41
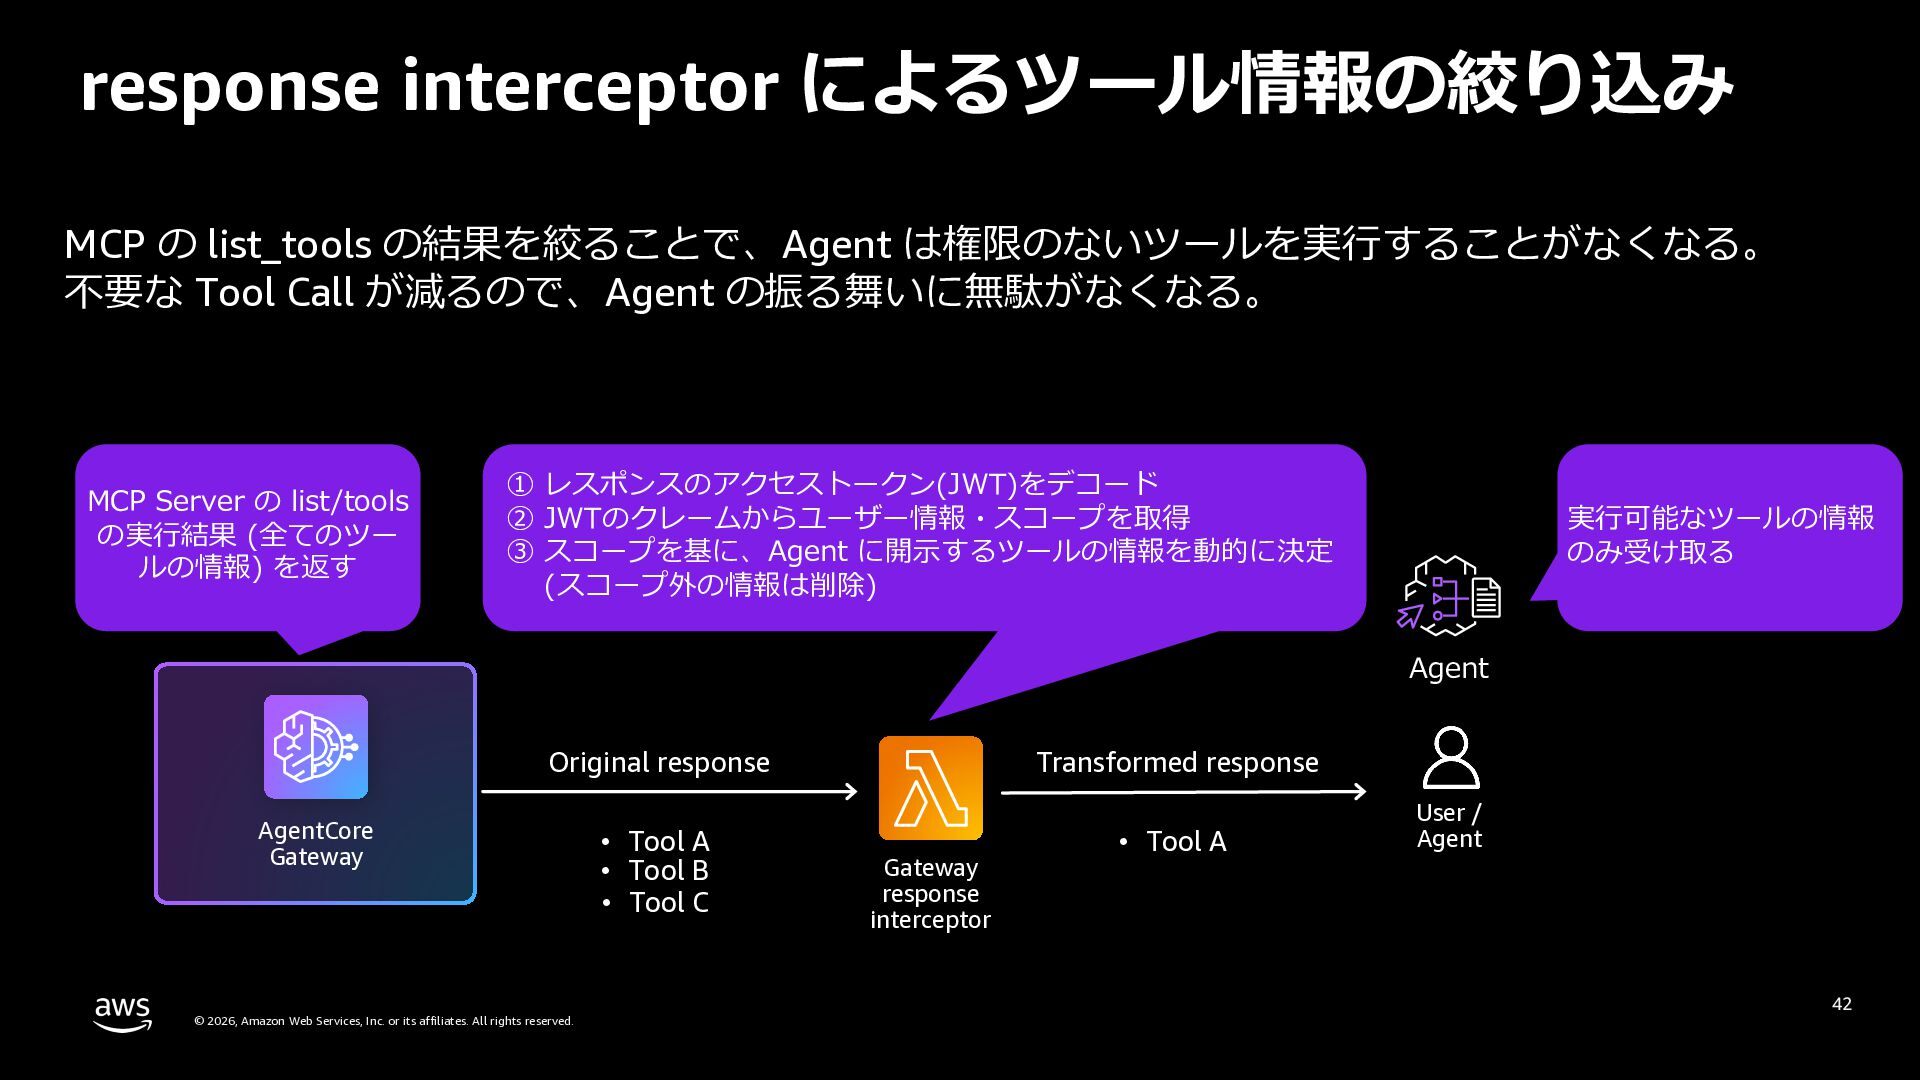
  34. response interceptor によるツール情報の絞り込み MCP の list_tools の結果を絞ることで、Agent は権限のないツールを実⾏することがなくなる。 不要な Tool

    Call が減るので、Agent の振る舞いに無駄がなくなる。 MCP Server の list/tools の実⾏結果 (全てのツー ルの情報) を返す ① レスポンスのアクセストークン(JWT)をデコード ② JWTのクレームからユーザー情報・スコープを取得 ③ スコープを基に、Agent に開⽰するツールの情報を動的に決定 (スコープ外の情報は削除) 実⾏可能なツールの情報 のみ受け取る Agent Original response AgentCore Gateway © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. • Tool A • Tool B • Tool C Transformed response Gateway response interceptor • Tool A User / Agent 42
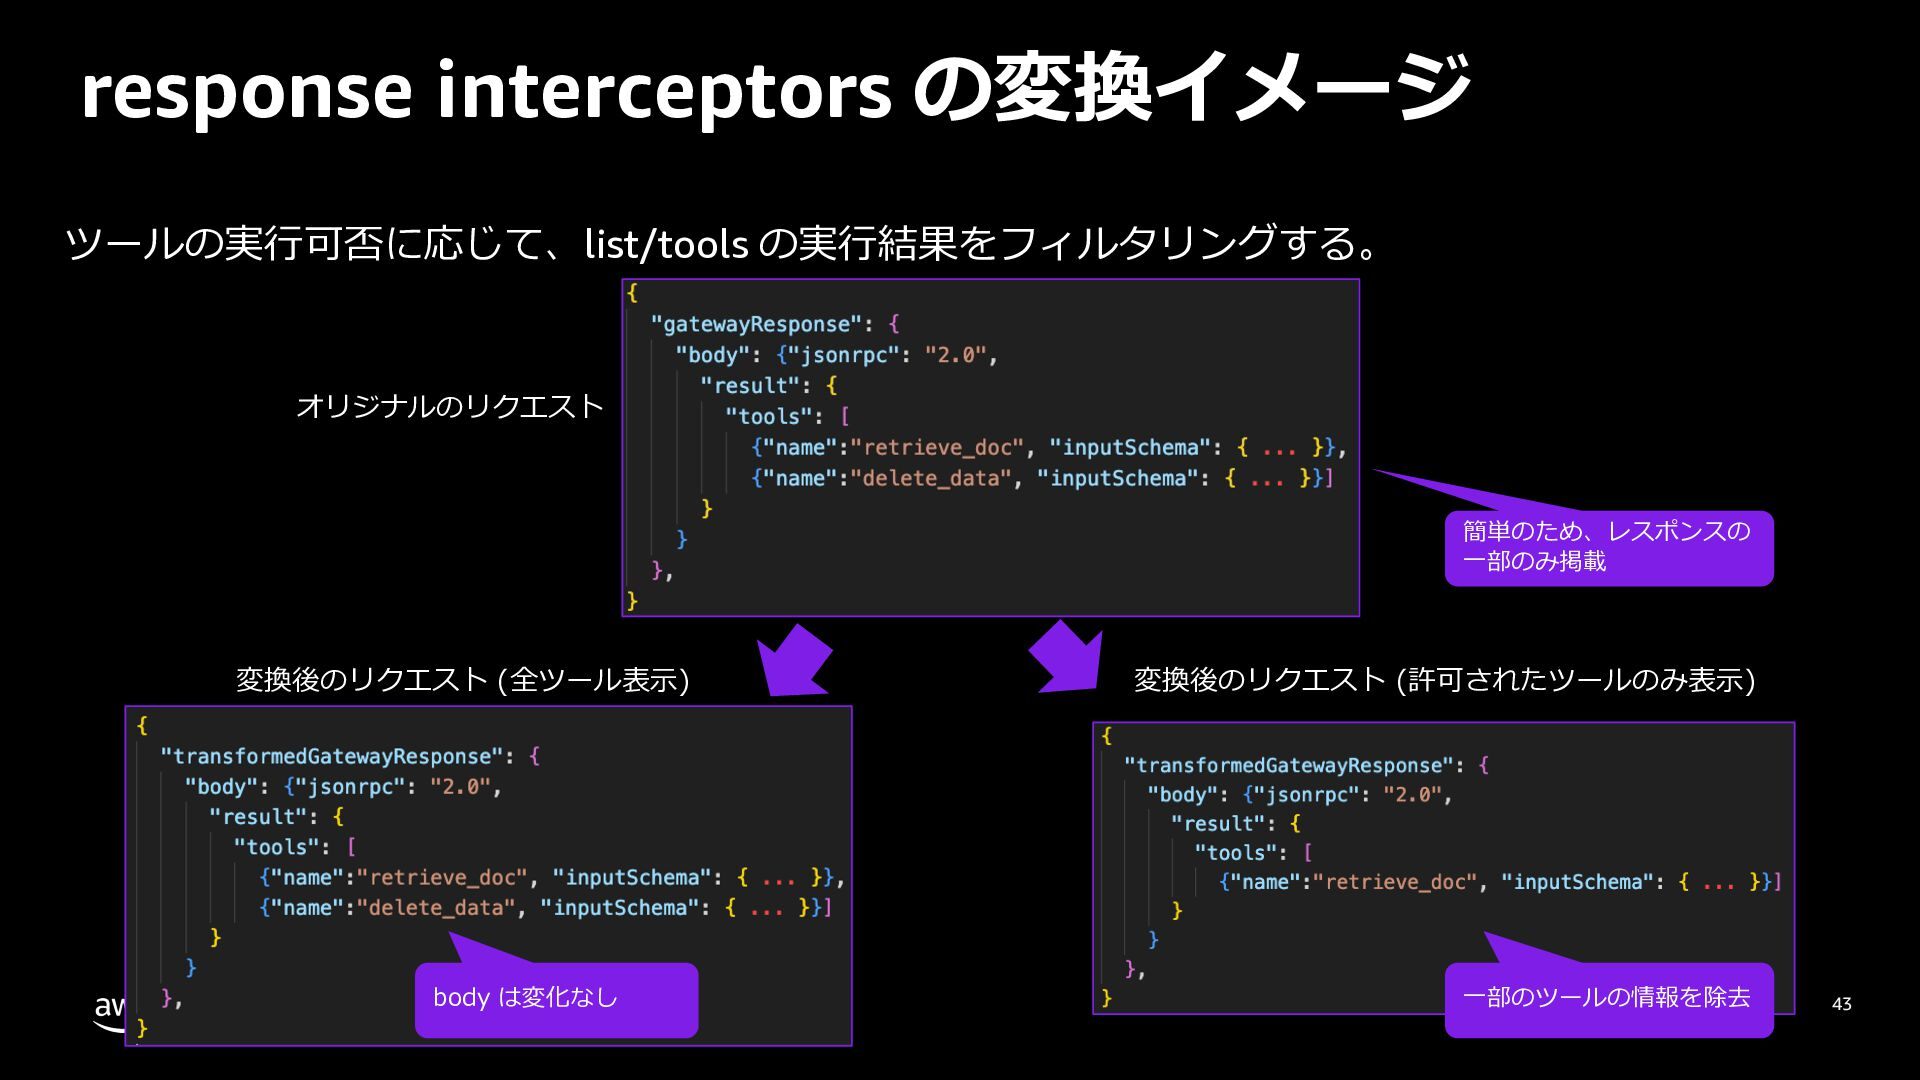
  35. response interceptors の変換イメージ ツールの実⾏可否に応じて、list/tools の実⾏結果をフィルタリングする。 オリジナルのレスポンス 簡単のため、レスポンスの ⼀部のみ掲載 変換後のレスポンス (全ツール表⽰)

    body は変化なし © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 変換後のレスポンス (許可されたツールのみ表⽰) ⼀部のツールの情報を除去 43
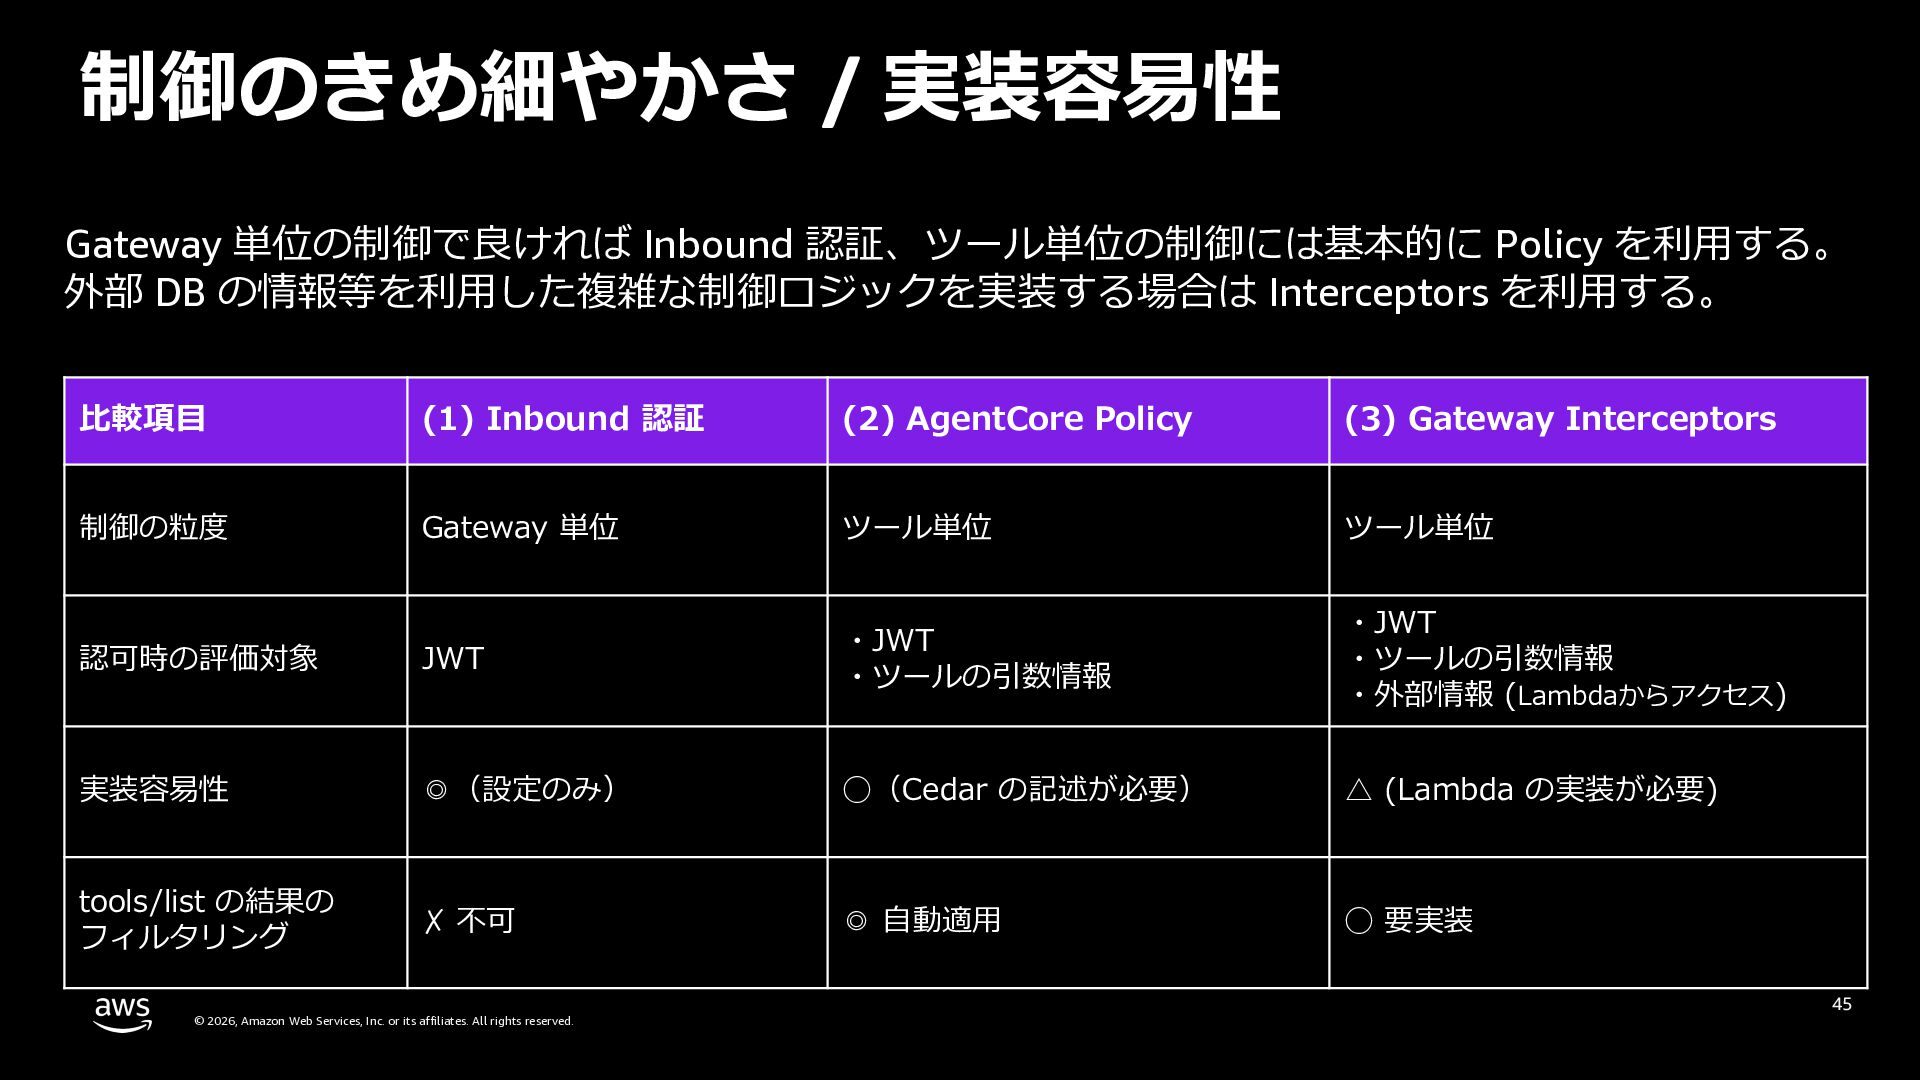
  36. 制御のきめ細やかさ / 実装容易性での⽐較 Gateway 単位の制御で良ければ Inbound 認証、ツール単位の制御には基本的に Policy を利⽤する。 外部

    DB の情報等を利⽤した複雑な制御ロジックを実装する場合は Interceptors を利⽤する。 ⽐較項⽬ (1) Inbound 認証 (2) AgentCore Policy (3) Gateway Interceptors 制御の粒度 Gateway 単位 ツール単位 ツール単位 認可時の評価対象 JWT ・JWT ・ツールの引数情報 ・JWT ・ツールの引数情報 ・外部情報 (Lambdaからアクセス) 実装容易性 ◎(設定のみ) ◯(Cedar の記述が必要) △ (Lambda の実装が必要) tools/list の結果の フィルタリング ✗ 不可 ◎ ⾃動適⽤ ◯ 要実装 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 45
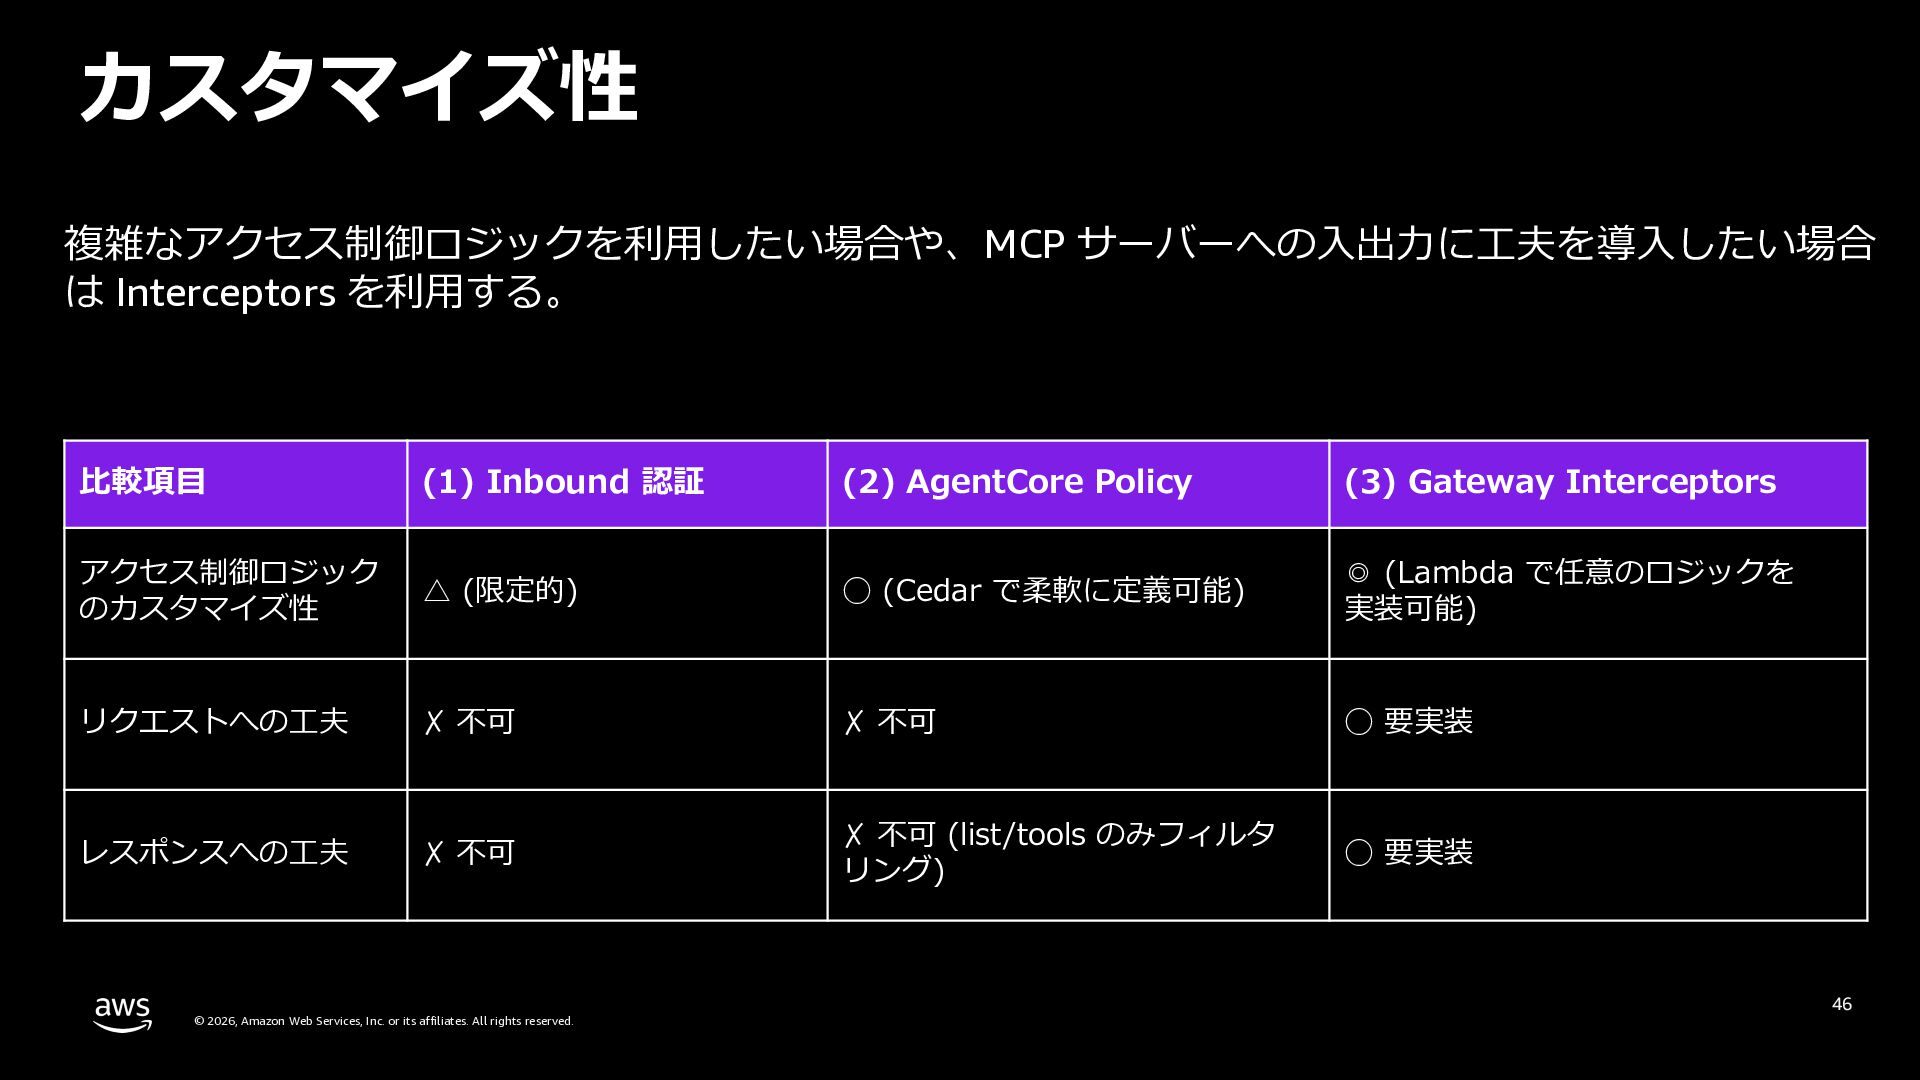
  37. カスタマイズ性での⽐較 複雑なアクセス制御ロジックを利⽤したい場合や、MCP サーバーへの⼊出⼒に⼯夫を導⼊したい場合 は Interceptors を利⽤する。 ⽐較項⽬ (1) Inbound 認証

    (2) AgentCore Policy (3) Gateway Interceptors アクセス制御ロジック のカスタマイズ性 △ (限定的) ◯ (Cedar で柔軟に定義可能) ◎ (Lambda で任意のロジックを 実装可能) リクエストへの⼯夫 ✗ 不可 ✗ 不可 ◯ 要実装 レスポンスへの⼯夫 ✗ 不可 ✗ 不可 (list/tools のみフィルタ リング) ◯ 要実装 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 46
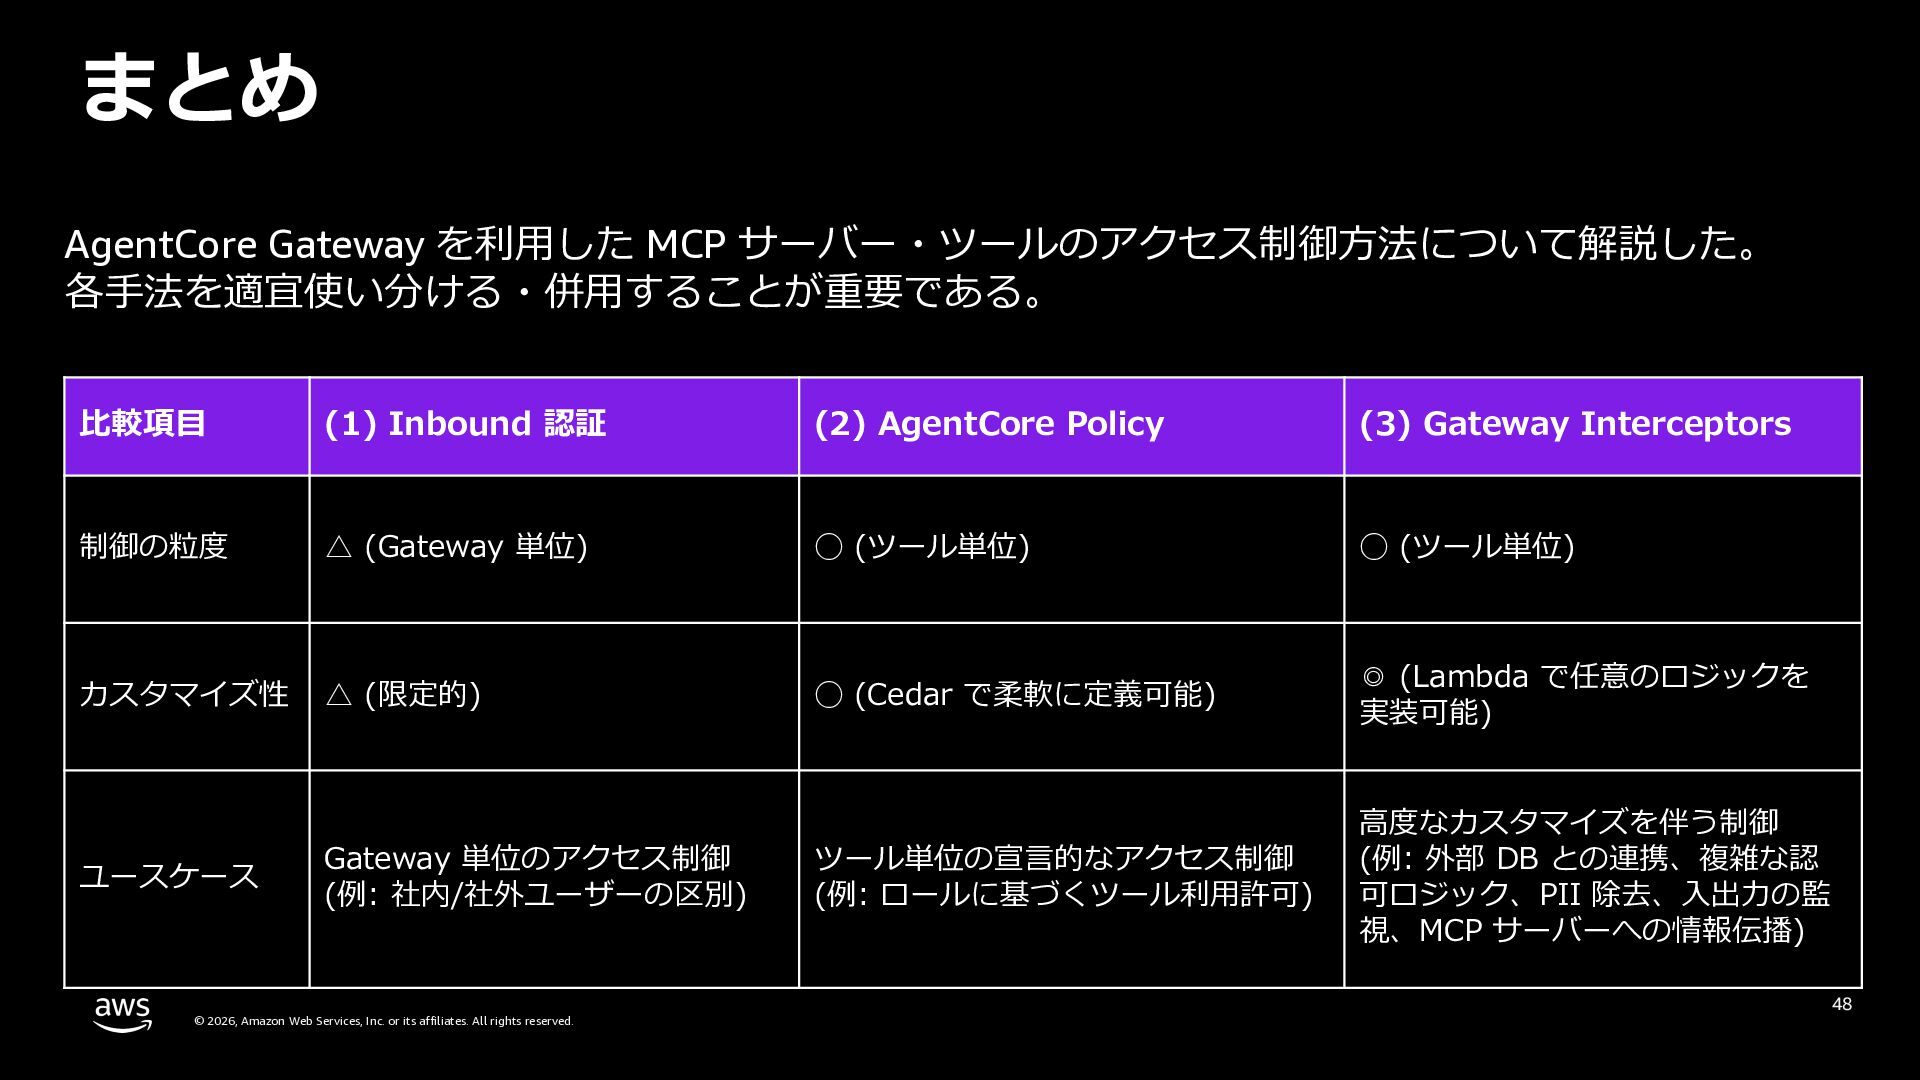
  38. まとめ AgentCore Gateway を利⽤した MCP サーバー・ツールのアクセス制御⽅法について解説した。 各⼿法を適宜使い分ける・併⽤することが重要である。 ⽐較項⽬ (1) Inbound

    認証 (2) AgentCore Policy (3) Gateway Interceptors 制御の粒度 △ (Gateway 単位) ◯ (ツール単位) ◯ (ツール単位) カスタマイズ性 △ (限定的) ◯ (Cedar で柔軟に定義可能) ◎ (Lambda で任意のロジックを 実装可能) ツール単位の宣⾔的なアクセス制御 (例: ロールに基づくツール利⽤許可) ⾼度なカスタマイズを伴う制御 (例: 外部 DB との連携、複雑な認 可ロジック、PII 除去、⼊出⼒の監 視、MCP サーバーへの情報伝播) ユースケース Gateway 単位のアクセス制御 (例: 社内/社外ユーザーの区別) © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 48
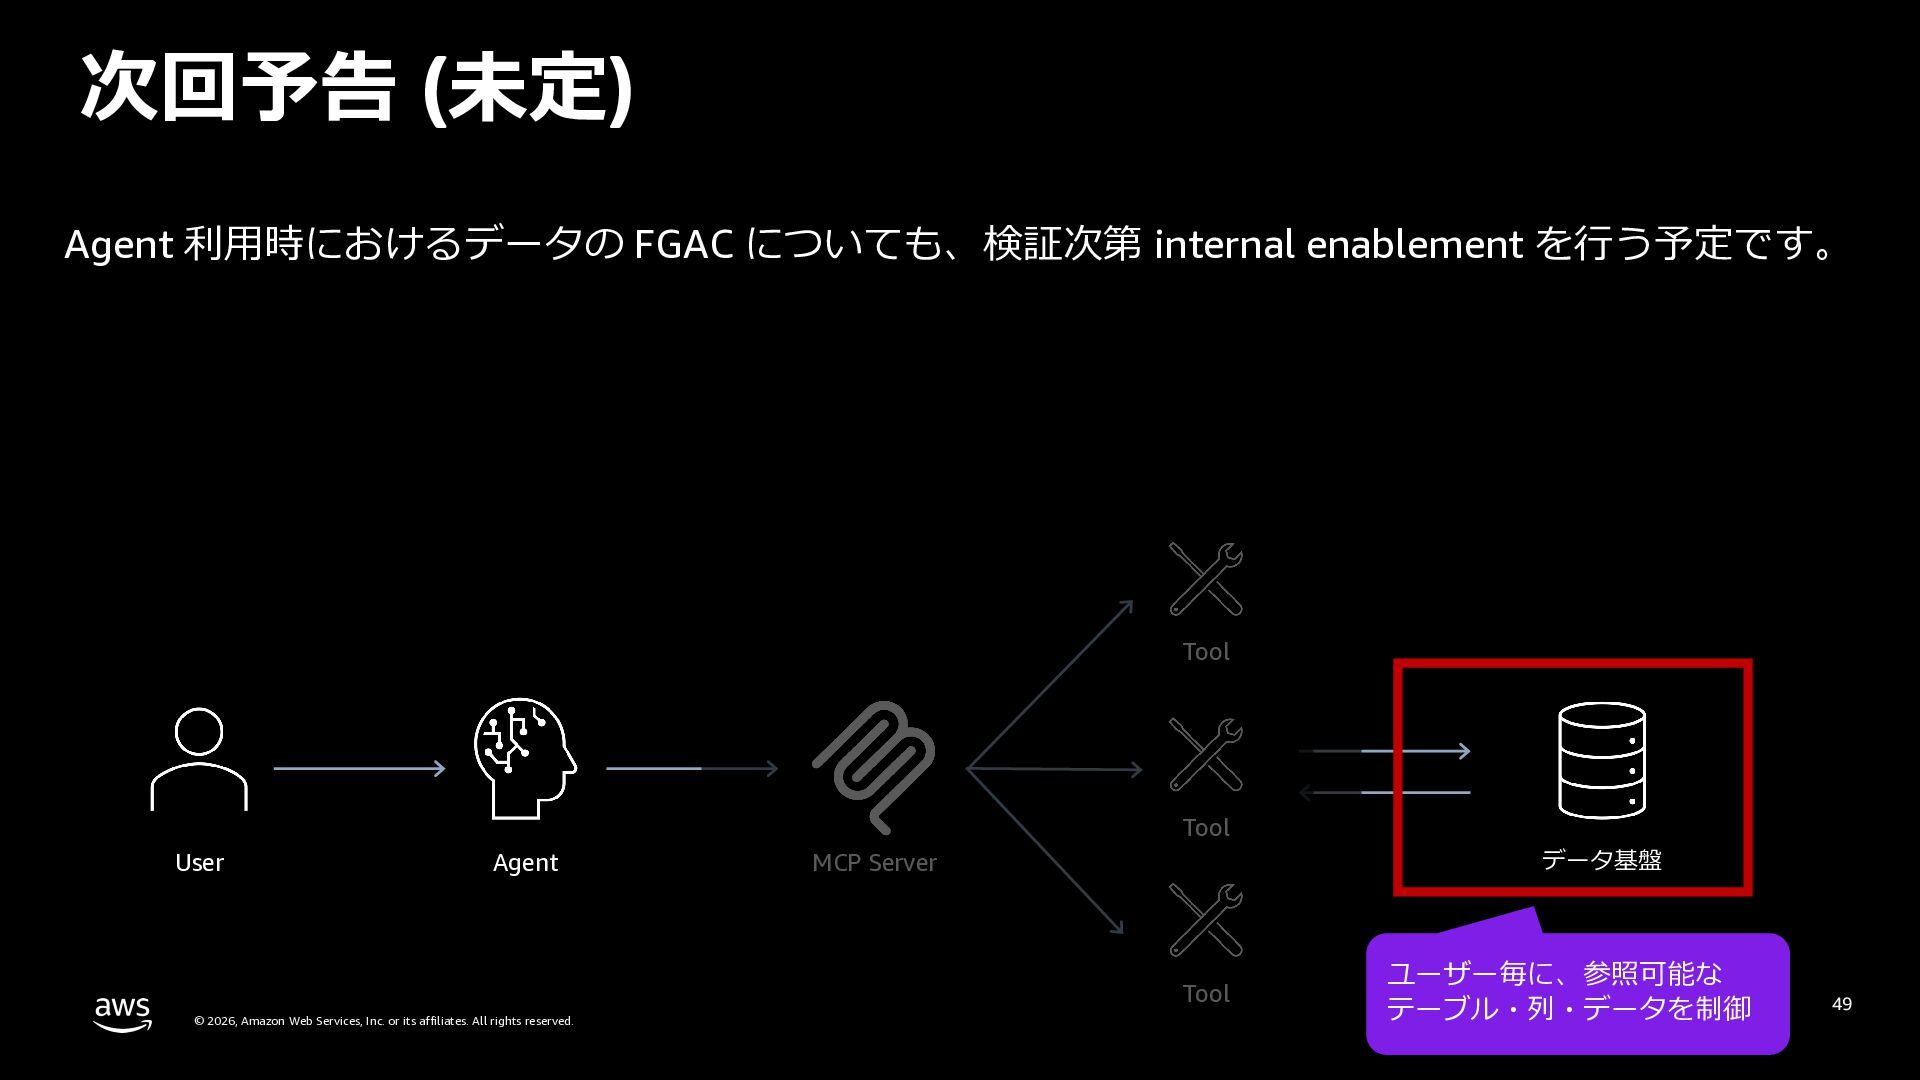
  39. 後編の範囲 Agent 利⽤時におけるデータの FGAC については、後編で解説します。 Tool Tool User Agent データ基盤

    MCP Server Tool © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ユーザー毎に、参照可能な テーブル・列・データを制御 49
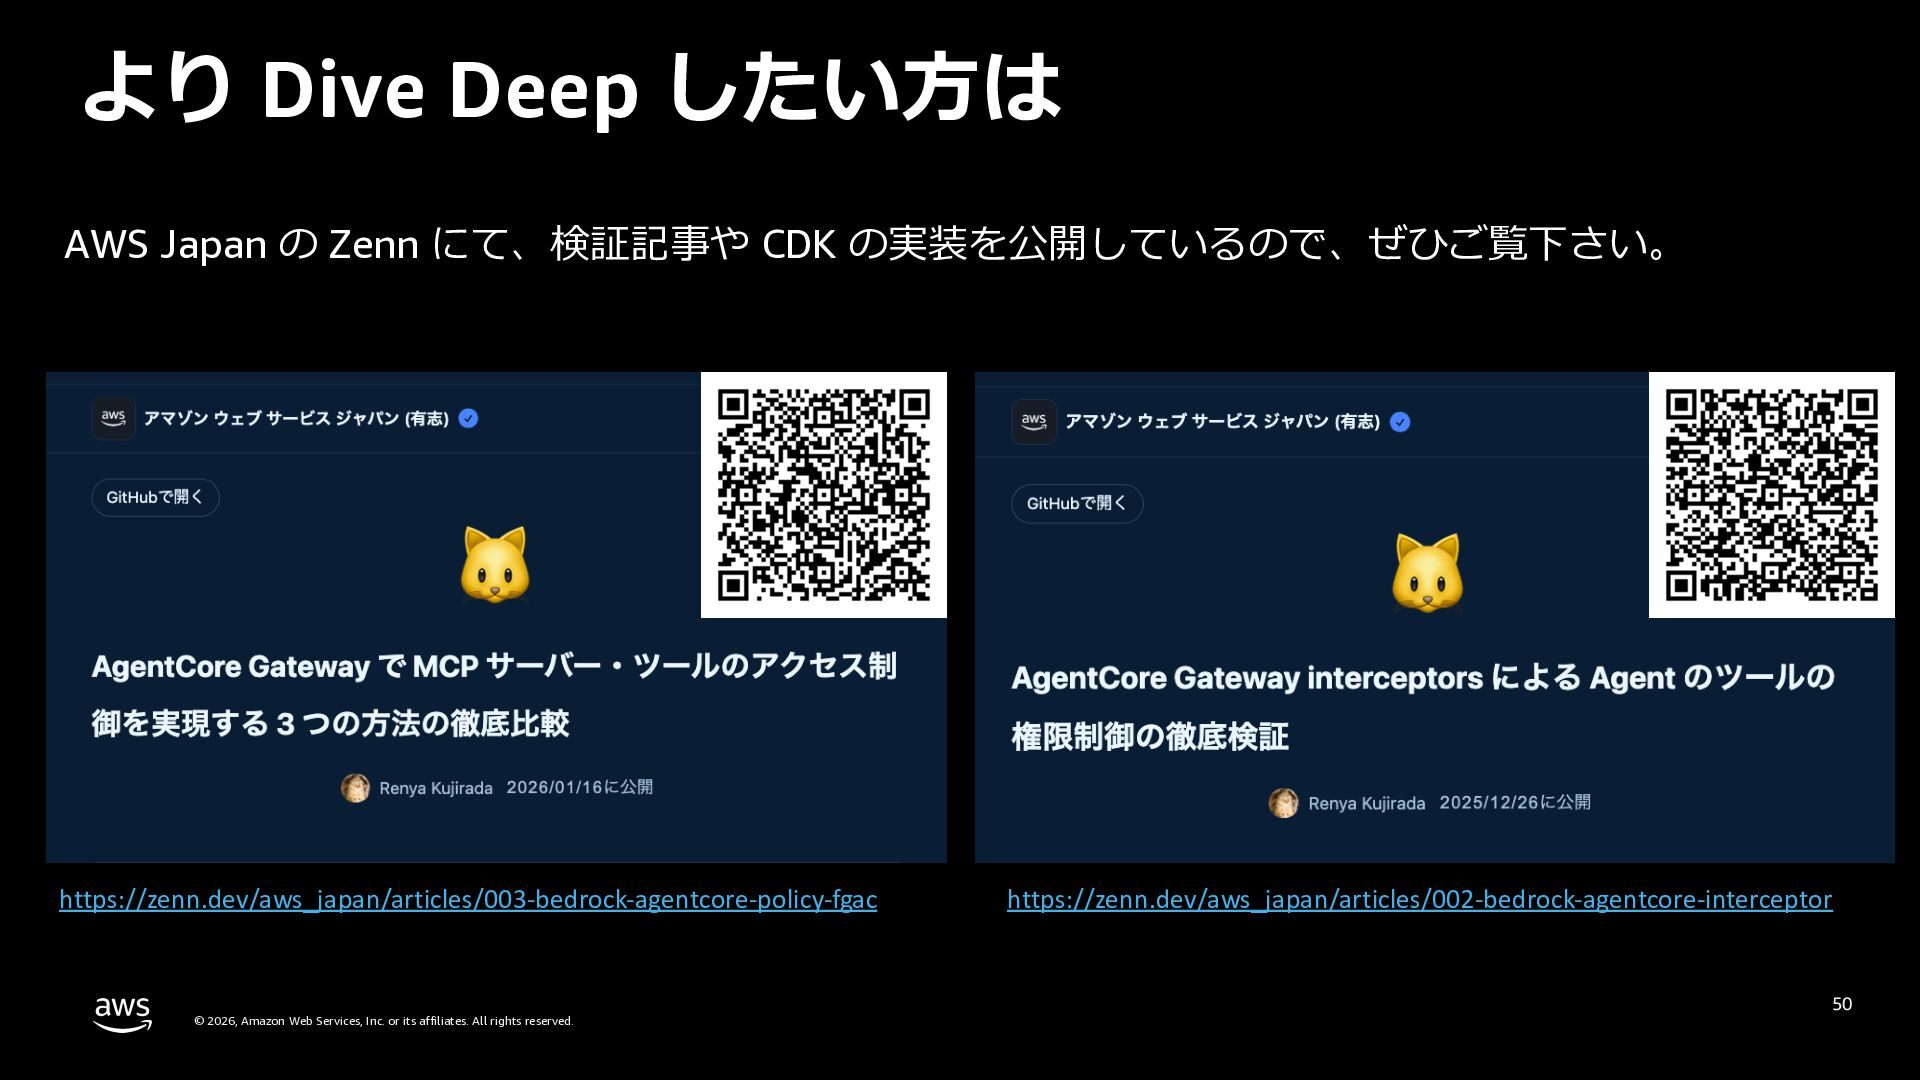
  40. より Dive Deep したい⽅は AWS Japan の Zenn にて、検証記事や CDK

    の実装を公開しているので、ぜひご覧下さい。 https://zenn.dev/aws_japan/articles/003-bedrock-agentcore-policy-fgac © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. https://zenn.dev/aws_japan/articles/002-bedrock-agentcore-interceptor 50
  41. Thank you! Renya Kujirada X: @recat_125 © 2026, Amazon Web

    Services, Inc. or its affiliates. All rights reserved. © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved.
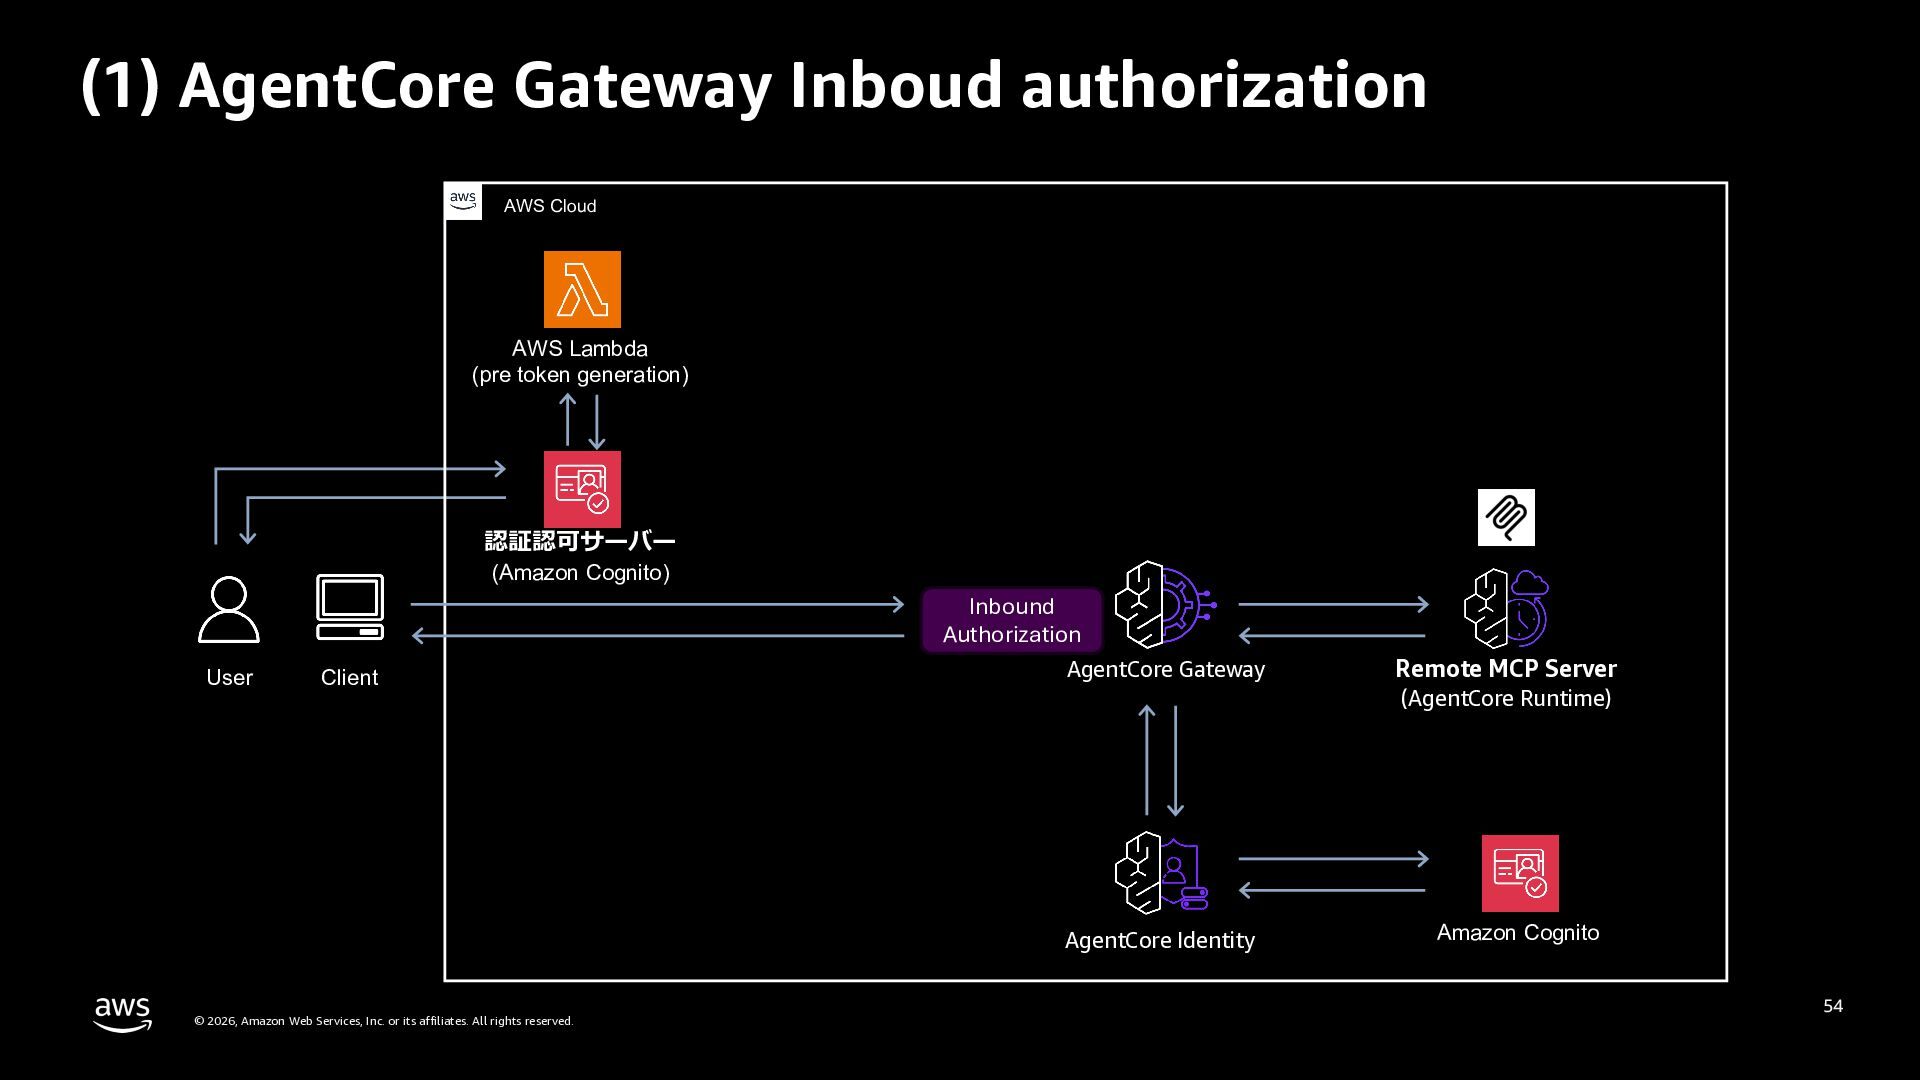
  42. (1) AgentCore Gateway Inboud authorization AWS Cloud AWS Lambda (pre

    token generation) 認証認可サーバー (Amazon Cognito) Inbound Authorization User Client AgentCore Gateway (AgentCore Runtime) AgentCore Identity © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Remote MCP Server Amazon Cognito 54
  43. (2) AgentCore Policy AWS Cloud AWS Lambda (pre token generation)

    AgentCore Policy 認証認可サーバー (Amazon Cognito) Inbound Authorization User Client AgentCore Gateway (AgentCore Runtime) AgentCore Identity © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Remote MCP Server Amazon Cognito 55
  44. (3) AgentCore Gateway interceptors AWS Cloud AWS Lambda (pre token

    generation) 入力 認証認可サーバー AWS Lambda (Interceptor) (Amazon Cognito) Inbound Authorization User AgentCore Gateway Client Remote MCP Server (AgentCore Runtime) 出力 AWS Lambda (Interceptor) AgentCore Identity © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Amazon Cognito 56
  45. MCPサーバー・ツールのアクセス制御⽅法 (1) Inbound authorization, (2) AgentCore Policy, (3) Gateway interceptors

    の 3 つに⼤別される。 (1) Inbound authorization (2) AgentCore Policy IdP IdP /mcp Request JWT /mcp scope: “read” tenant_id: ABC JWT authorizer JWT authorizer AgentCore Runtime & Gateway ⼤まか refund: $200 Allow if tenant_id=“ABC” Allow if tenant_id=“ABC” AgentCore Identity © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. (3) Gateway interceptors IdP JWT group: “Admin” scope: “read” tenant_id: ABC Allow if refund < 100 and group=“Admin AgentCore Gateway AgentCore Policy 制御の粒度 Request /mcp refund: $200 Allow if tenant_id=“ABC” JWT authorizer JWT group: “Admin” scope: “read” tenant_id: ABC Gateway interceptors Tools access control, schema translation, data sanitization AgentCore Gateway 細かい 58
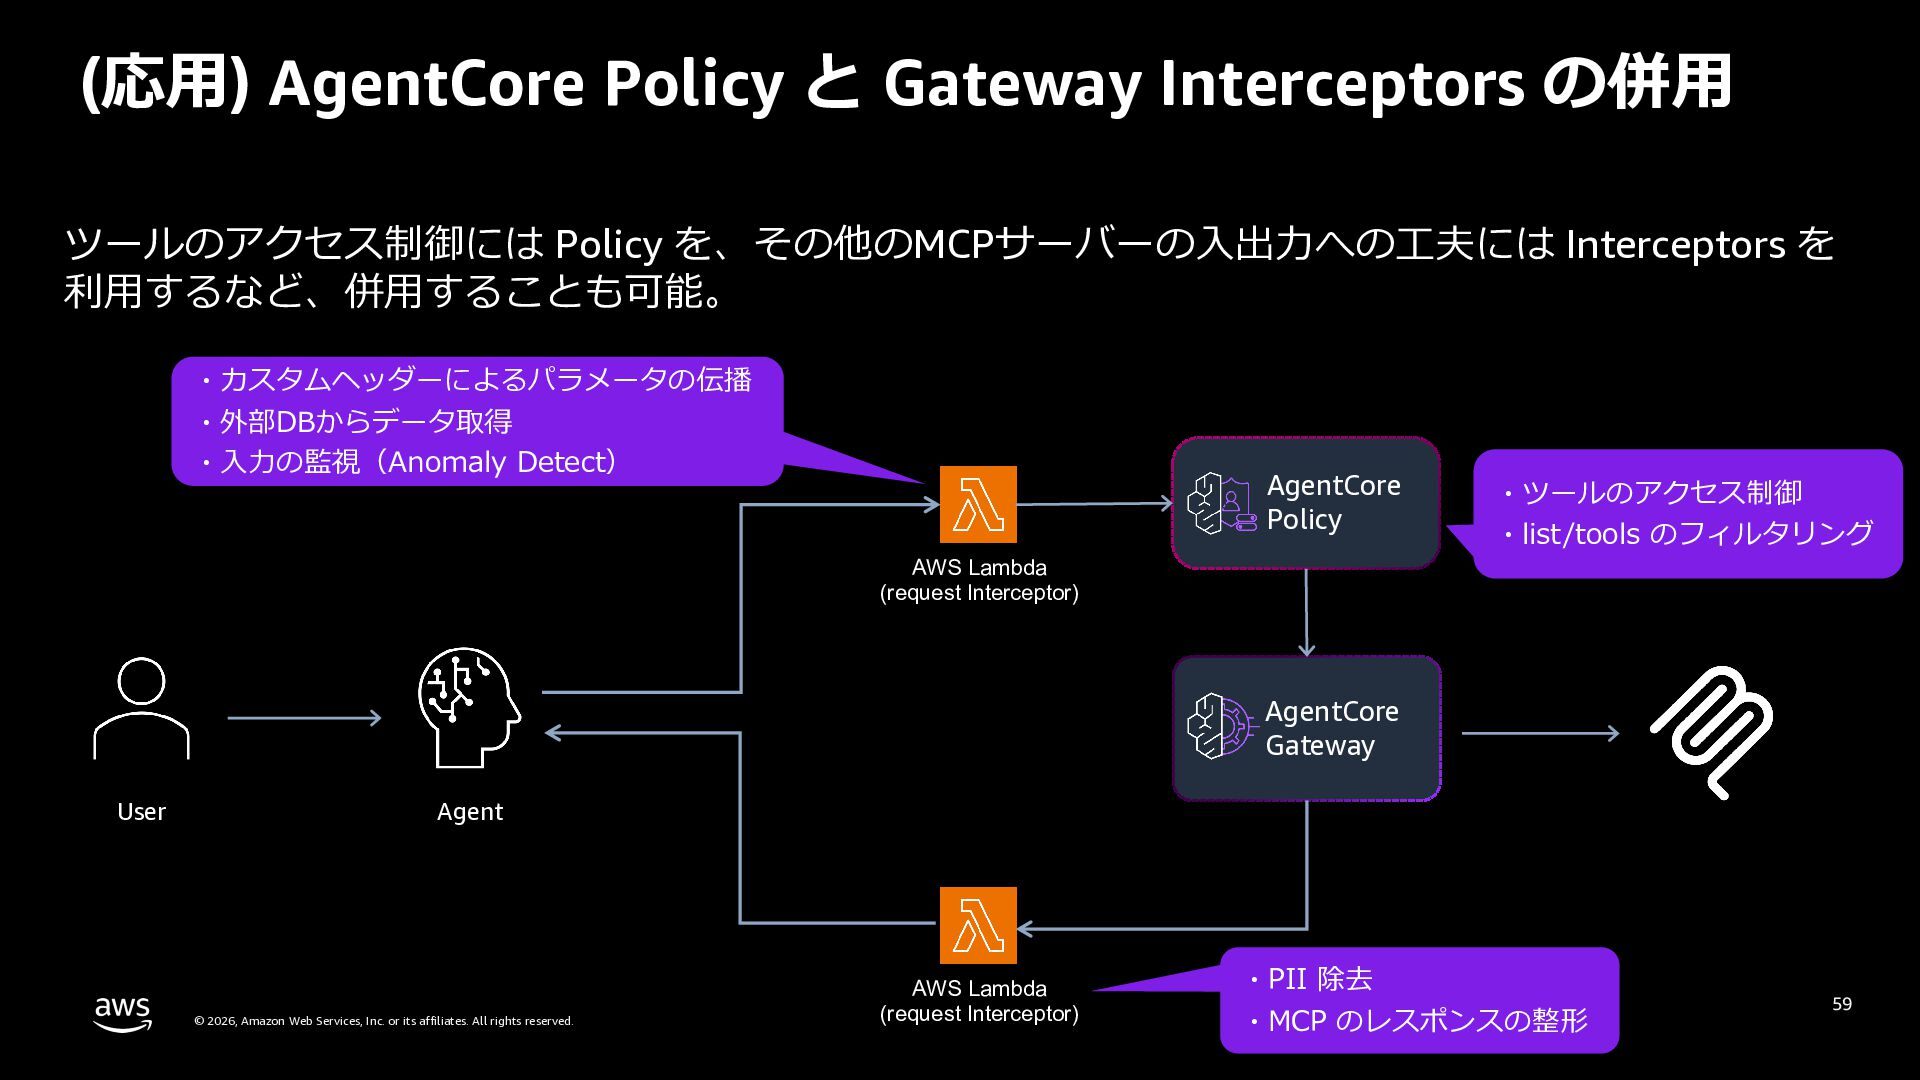
  46. (応⽤) AgentCore Policy と Gateway Interceptors の併⽤ ツールのアクセス制御には Policy を、その他のMCPサーバーの⼊出⼒への⼯夫には

    Interceptors を 利⽤するなど、併⽤することも可能。 ・カスタムヘッダーによるパラメータの伝播 ・外部DBからデータ取得 ・⼊⼒の監視(Anomaly Detect) AgentCore Policy AWS Lambda (request Interceptor) ・ツールのアクセス制御 ・list/tools のフィルタリング AgentCore Gateway User Agent © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AWS Lambda (request Interceptor) ・PII 除去 ・MCP のレスポンスの整形 59