Share
Embed
AIエージェントの権限管理 2: データ基盤の Fine grained access control 編
AWS PartnerCast - 1 Day Solution Dive Deep 登壇資料。2026/6/12
AIエージェントの権限管理 1: MCPサーバー・ツールの Fine grained access control 編 の続編です。
マルチテナントなデータ基盤で、 Agent が MCP Server 経由でデータ基盤にアクセスする際に、テナント毎のデータアクセスを制御する方法を解説します。
Agent に見せる(アクセスさせる)データをユーザーごとに制御する方法について、AgentCore (Gateway Interceptor, Gateway Header Propagation) や MCP Server でどのように実現するかを整理してます。

Renya Kujirada
April 17, 2026
Transcript
48 slides
-
UPDATE THIS PRESENTATION HEADER IN SLIDE MASTER AI エージェントの権限管理 2:
データ基盤の Fine grained access control 編 鯨⽥ 連也 AI/ML Specialist Solutions Architect 2026/06/12 © 2026, Amazon Web © 2026, Services, Amazon Inc. or Web its Services, affiliates.Inc. All or rights its affiliates. reserved.All Amazon rights reserved. Confidential Amazon and Trademark. Confidential and Trademark. -
⾃⼰紹介 鯨⽥ 連也 アマゾン ウェブ サービス ジャパン合同会社 スペシャリスト ソリューションアーキテクト, AI/ML
前職 (NTT DATA) では、データサイエンティストとして、 深層学習モデル (Computer Vision)・AI Agent の開発に従事。 • 興味: AI Agent 開発, LLM 学習・推論 X: @recat_125 • 好きなサービス: Amazon Bedrock, Amazon SageMaker AI © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 2 -
発表の背景と⽬的 今後、企業毎に数百・数千の Agent がデプロイされ、Agent が社内の多数のデータソースや API と 接続するようなことが多くなると考えられる。 セキュアに Agent
にツールやデータを利⽤させるには Fine-grained access control (FGAC) が重要で ある。AgentCore を利⽤することで、FGAC を容易に実装できる。 本発表では、AgentCore を利⽤したデータの FGAC の実装パターンについて、Dive Deep する。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 3 -
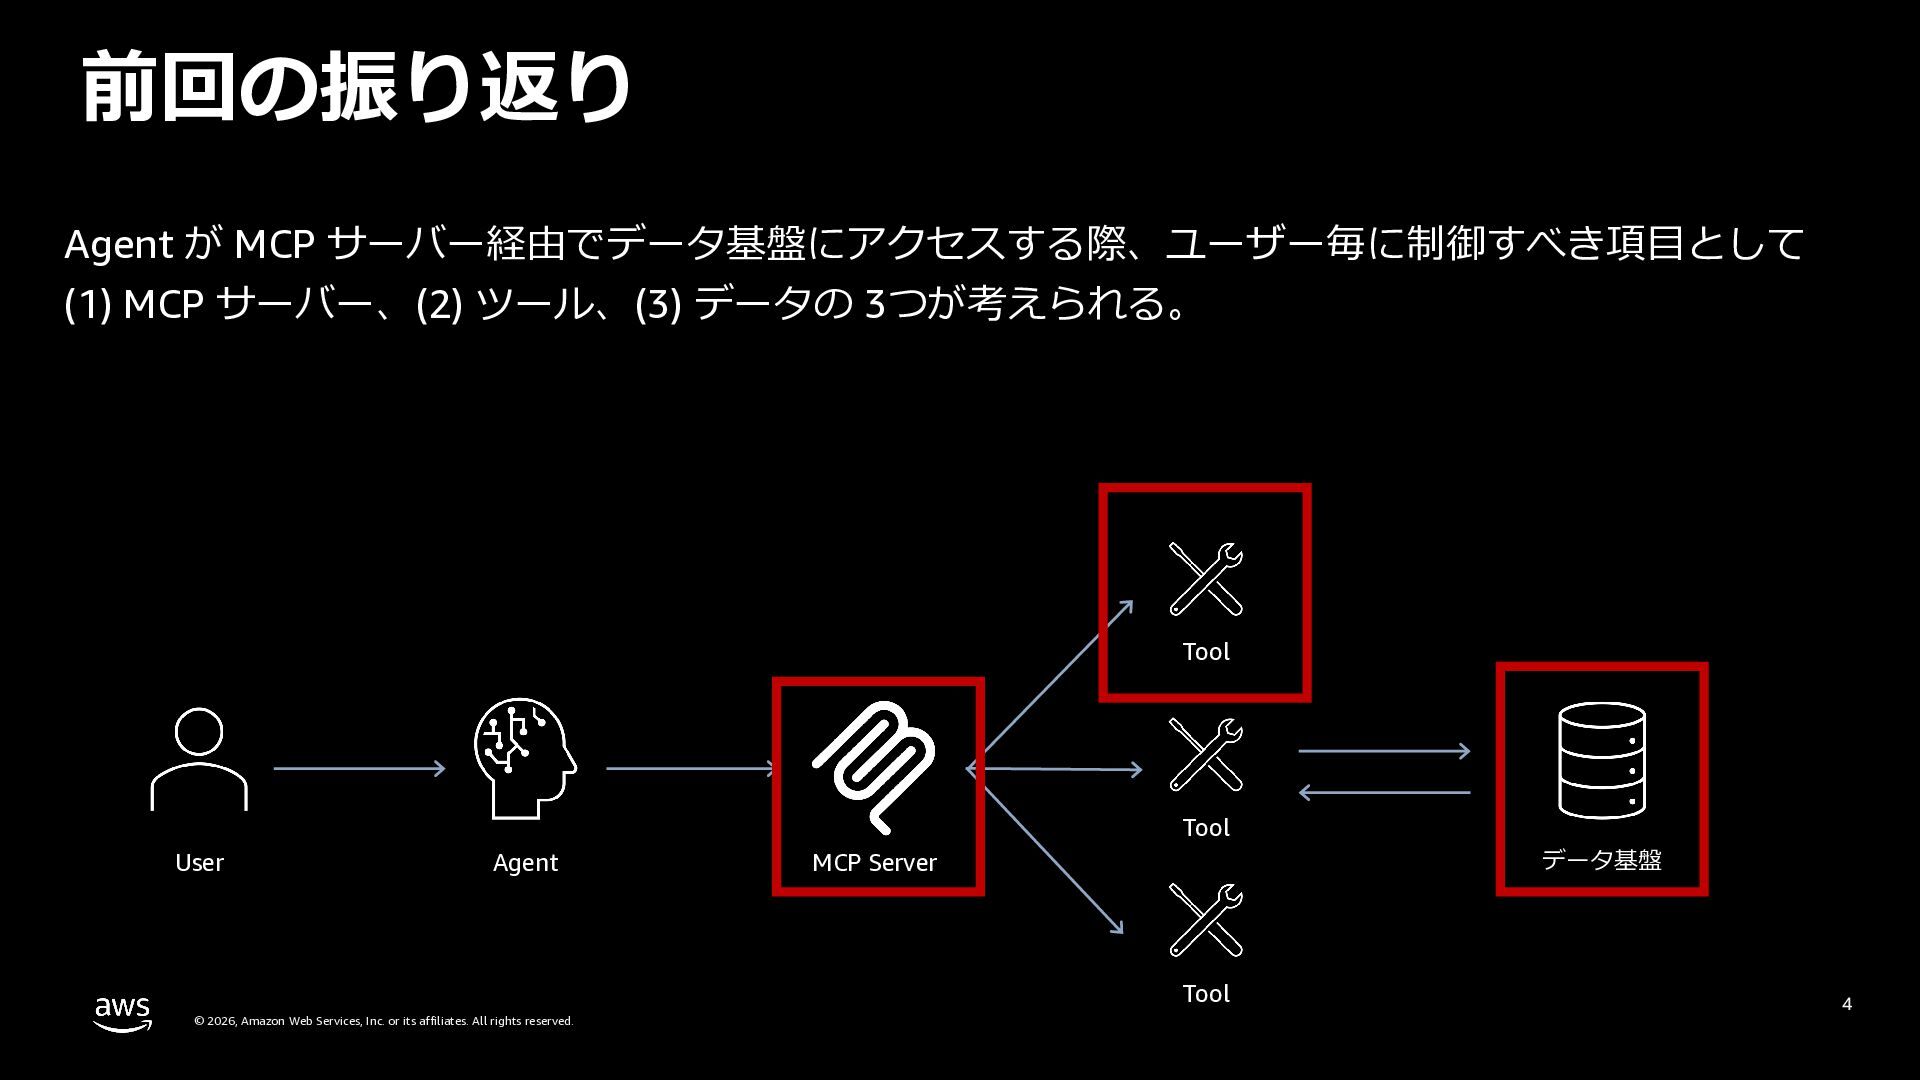
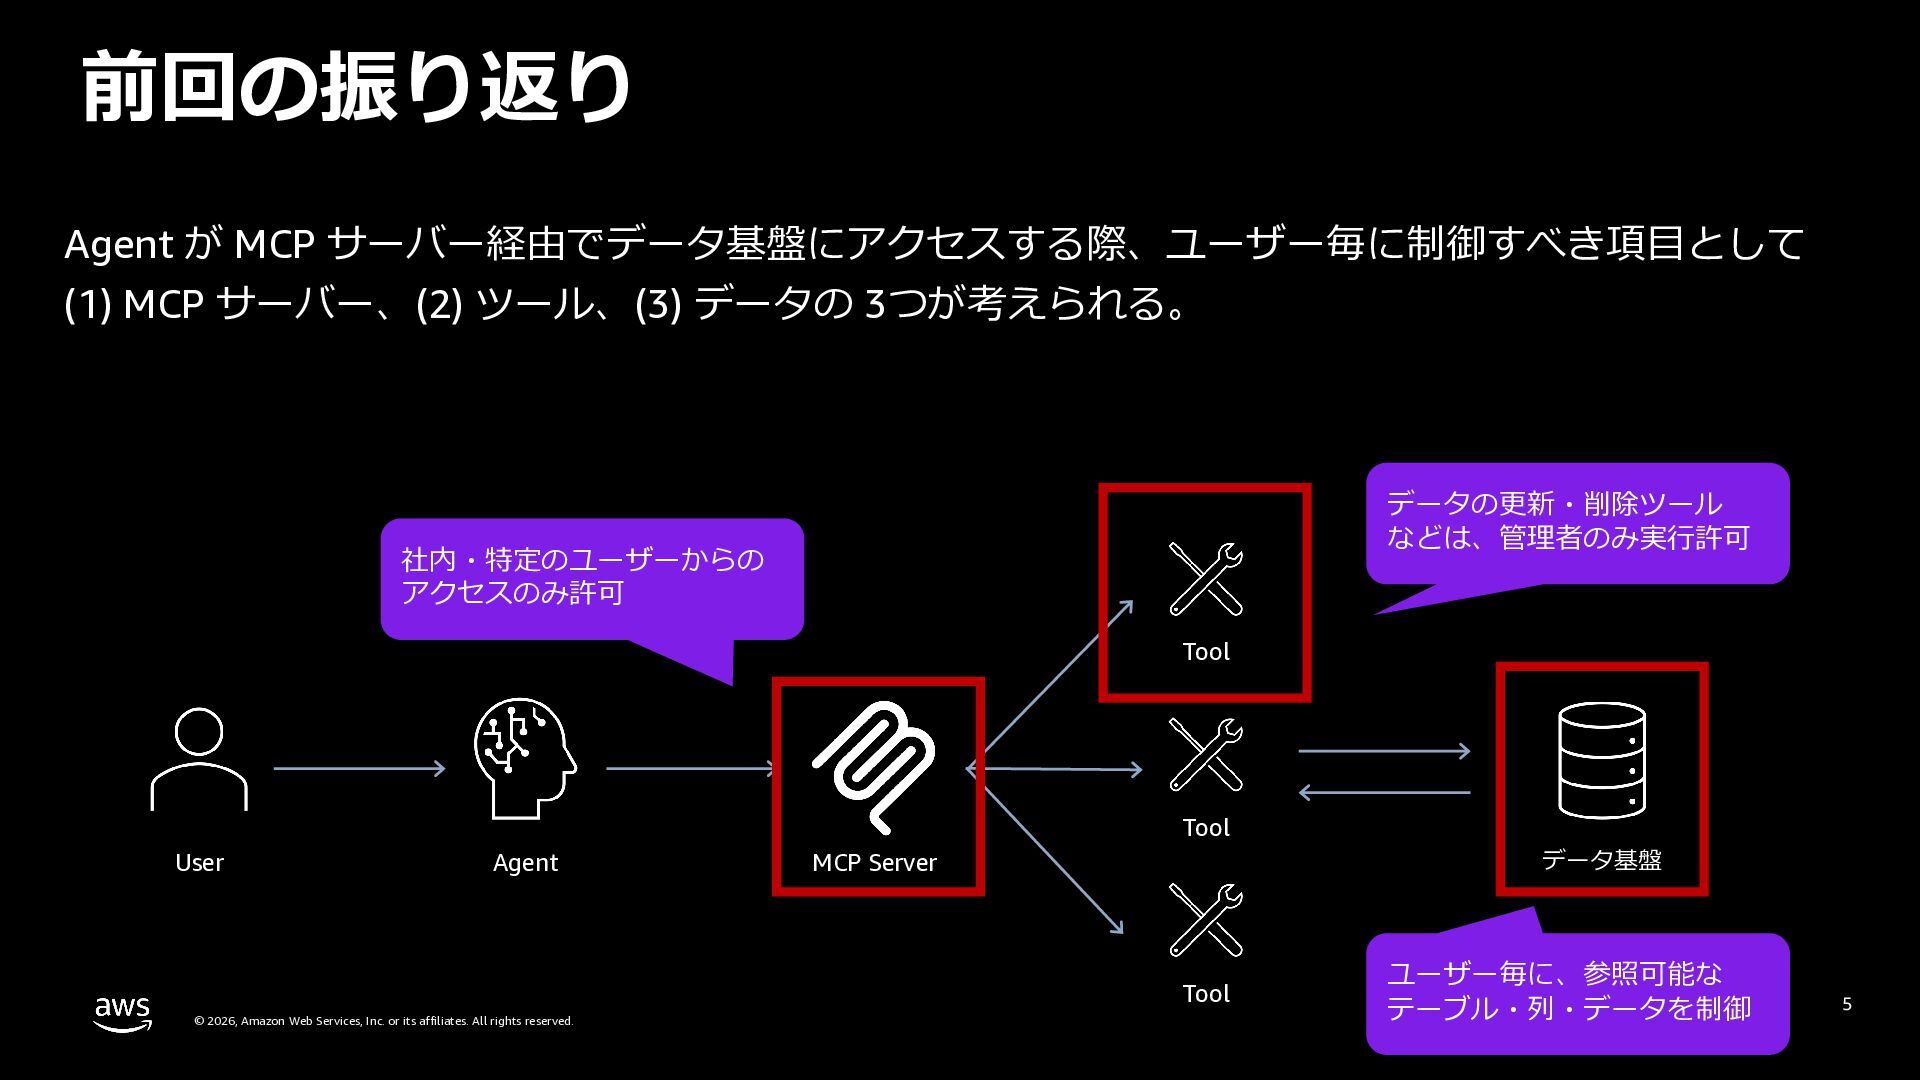
前編の振り返り Agent が MCP サーバー経由でデータ基盤にアクセスする際、ユーザー毎に制御すべき項⽬として (1) MCP サーバー、(2) ツール、(3) データの
3つが考えられる。 Tool Tool User Agent データ基盤 MCP Server Tool © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 4 -
前編の振り返り Agent が MCP サーバー経由でデータ基盤にアクセスする際、ユーザー毎に制御すべき項⽬として (1) MCP サーバー、(2) ツール、(3) データの
3つが考えられる。 データの更新・削除ツール などは、管理者のみ実⾏許可 社内・特定のユーザーからの アクセスのみ許可 Tool Tool User Agent データ基盤 MCP Server Tool © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ユーザー毎に、参照可能な テーブル・列・データを制御 5 -
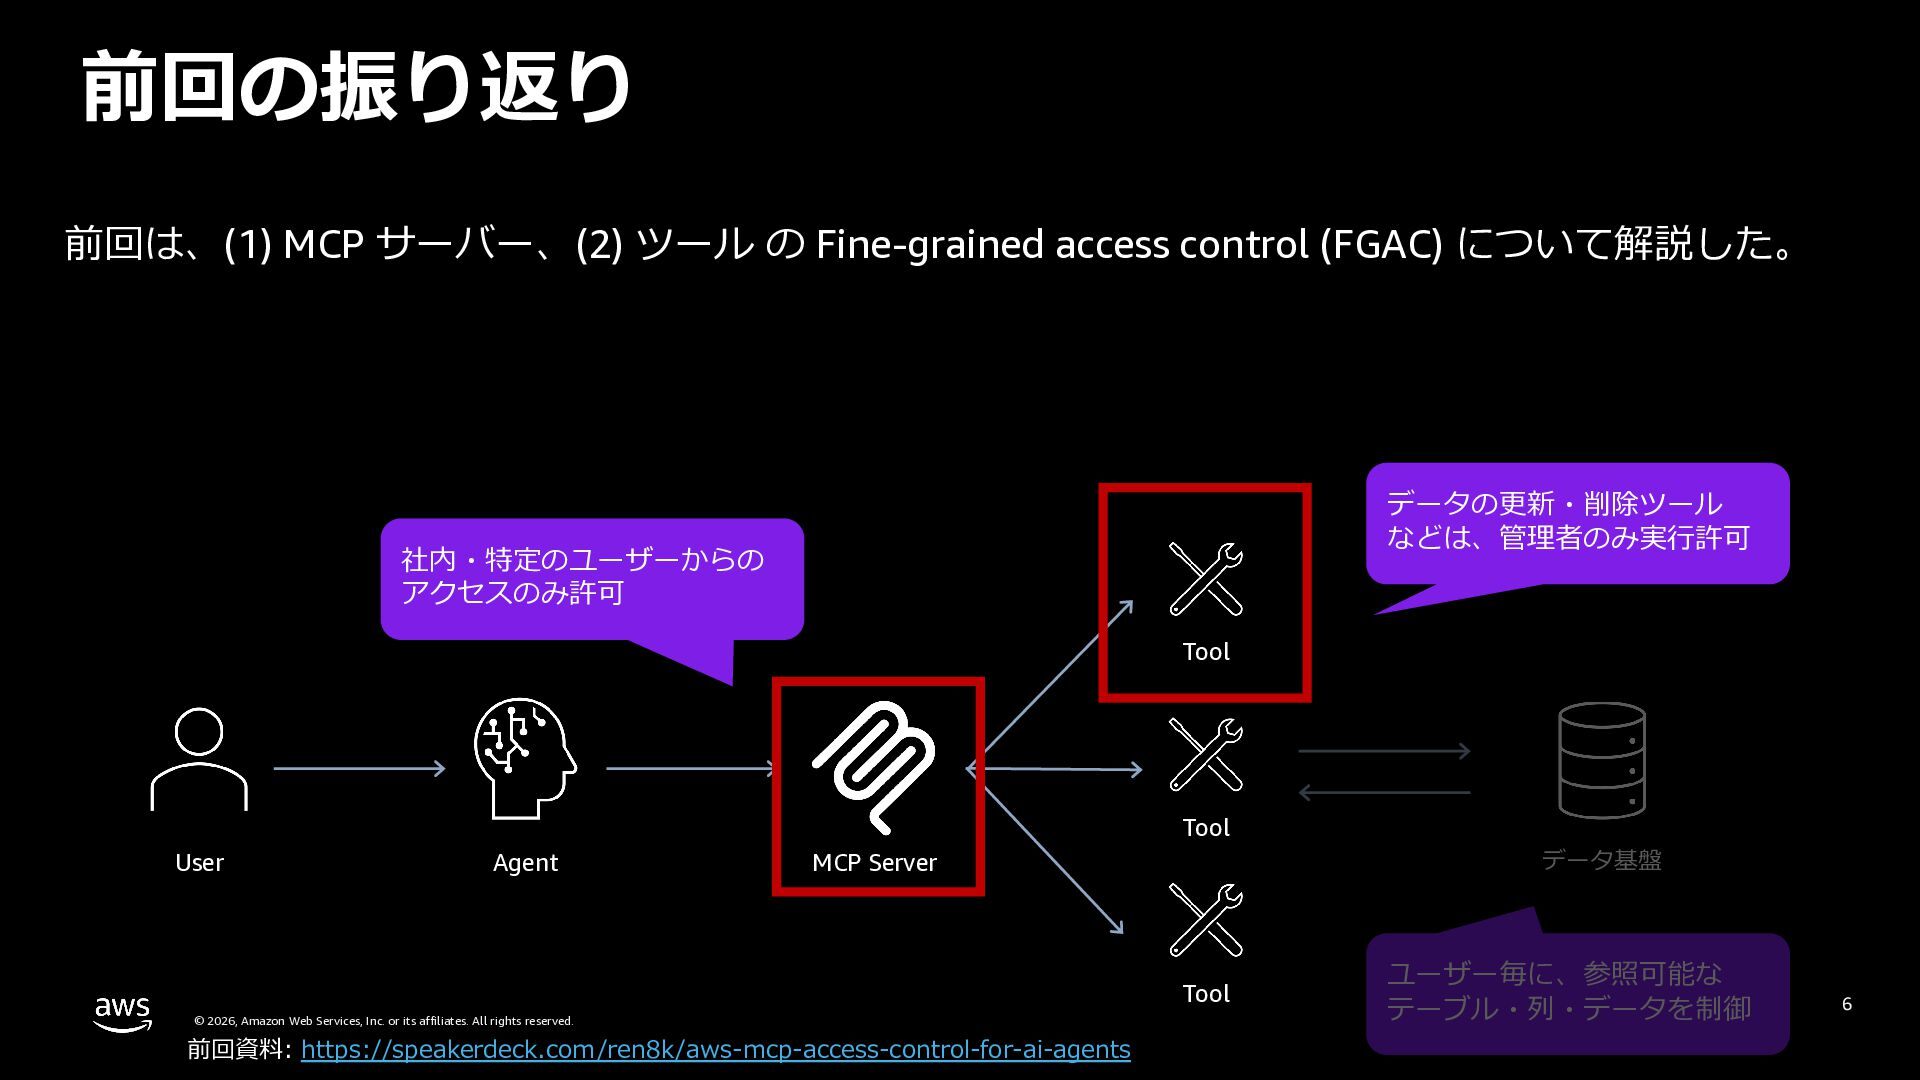
前編の振り返り 前回は、(1) MCP サーバー、(2) ツール の Fine-grained access control (FGAC)
について解説した。 データの更新・削除ツール などは、管理者のみ実⾏許可 社内・特定のユーザーからの アクセスのみ許可 Tool Tool User Agent データ基盤 MCP Server Tool © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ユーザー毎に、参照可能な テーブル・列・データを制御 6 -
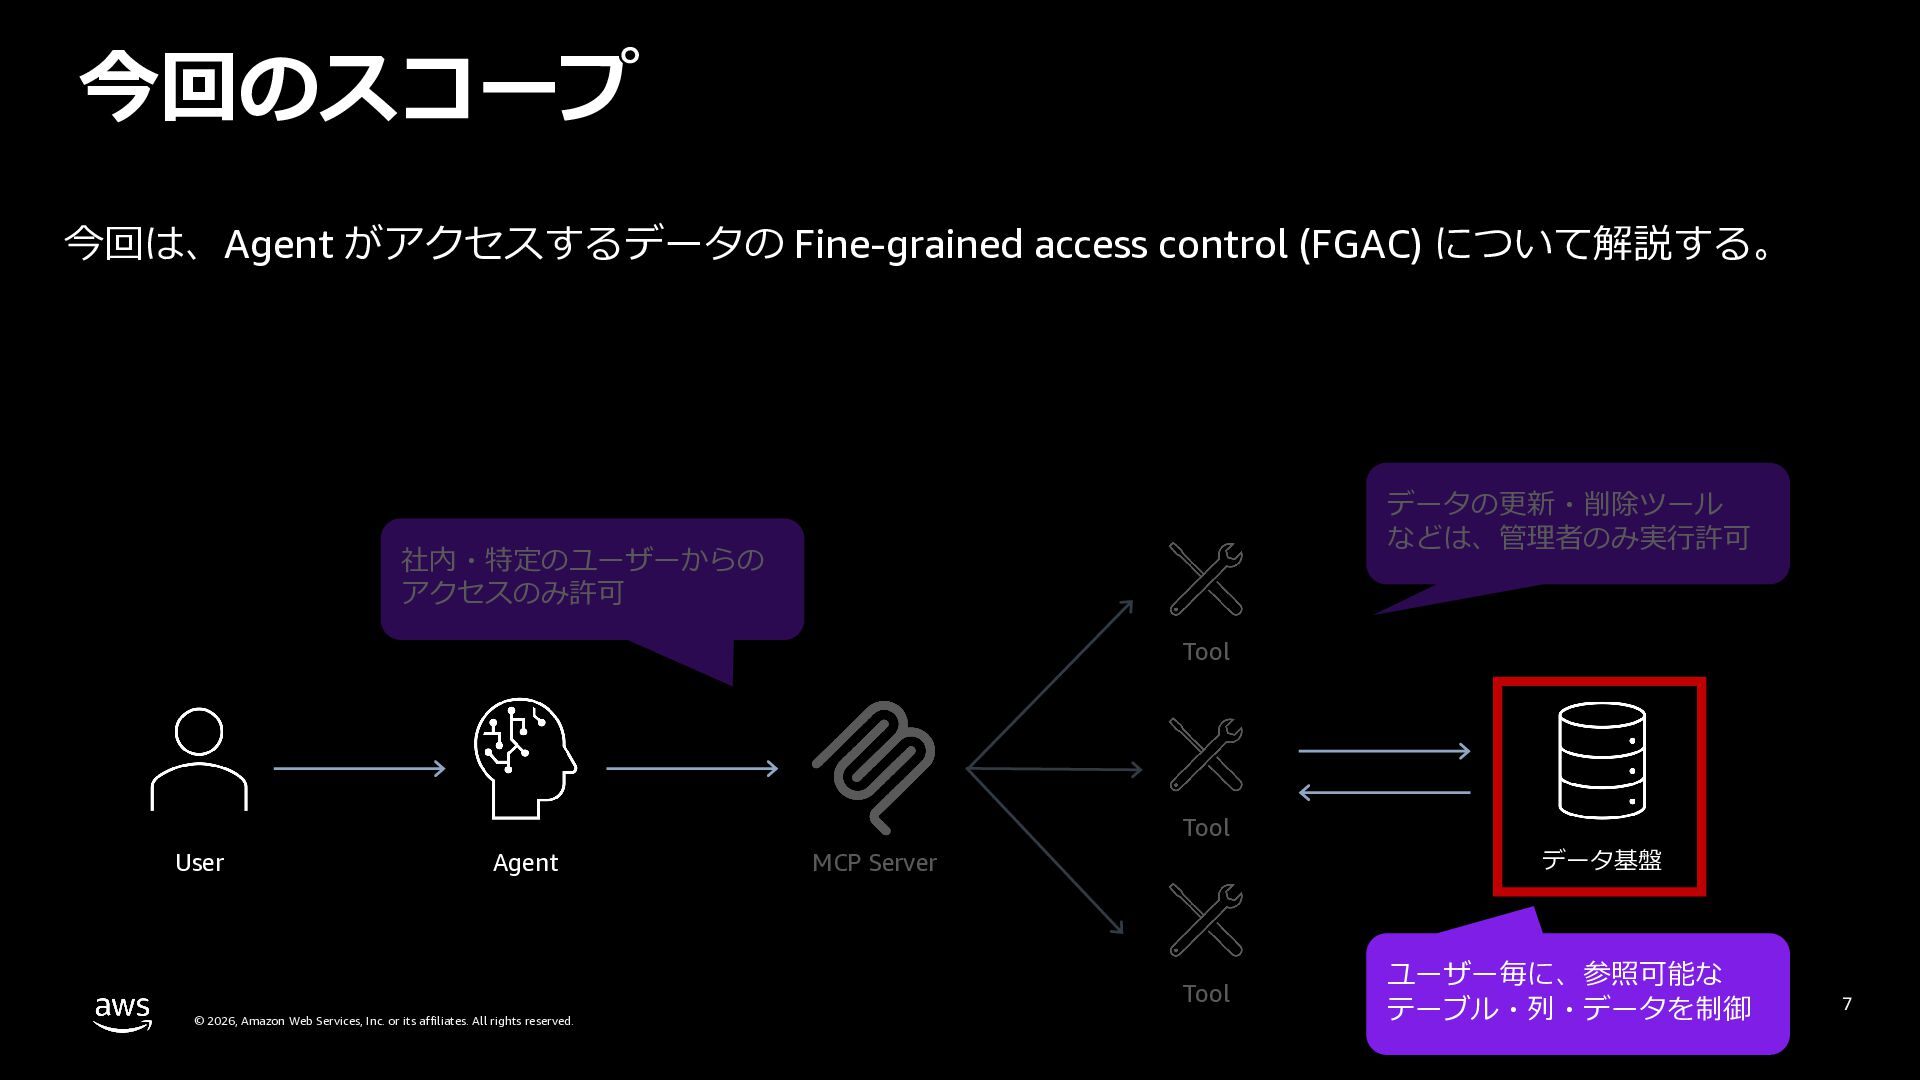
後編のスコープ 今回は、Agent がアクセスするデータの Fine-grained access control (FGAC) について解説する。 データの更新・削除ツール などは、管理者のみ実⾏許可
社内・特定のユーザーからの アクセスのみ許可 Tool Tool User Agent データ基盤 MCP Server Tool © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ユーザー毎に、参照可能な テーブル・列・データを制御 7 -
発表のゴールとレベル • ゴール︓AgentCore を利⽤した、Agent がアクセスするデータの FGAC の実現⽅法を理解する • レベル︓L300 ~
L400 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 8 -
アジェンダ • Agent がアクセスするデータの FGAC の重要性 • AgentCore Gateway の前提知識
• AgentCore Gateway を利⽤したデータ基盤の FGAC アーキテクチャ • 本発表のユースケース: AgentCore x Lake Formation によるデータの FGAC • AgentCore Gateway カスタムヘッダー伝播の Dive Deep • まとめ © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 9 -
Agent がアクセスするデータの Fine-grained access control (FGAC) の重要性 © 2026, Amazon
Web Services, Inc. or its affiliates. All rights reserved. 10 -
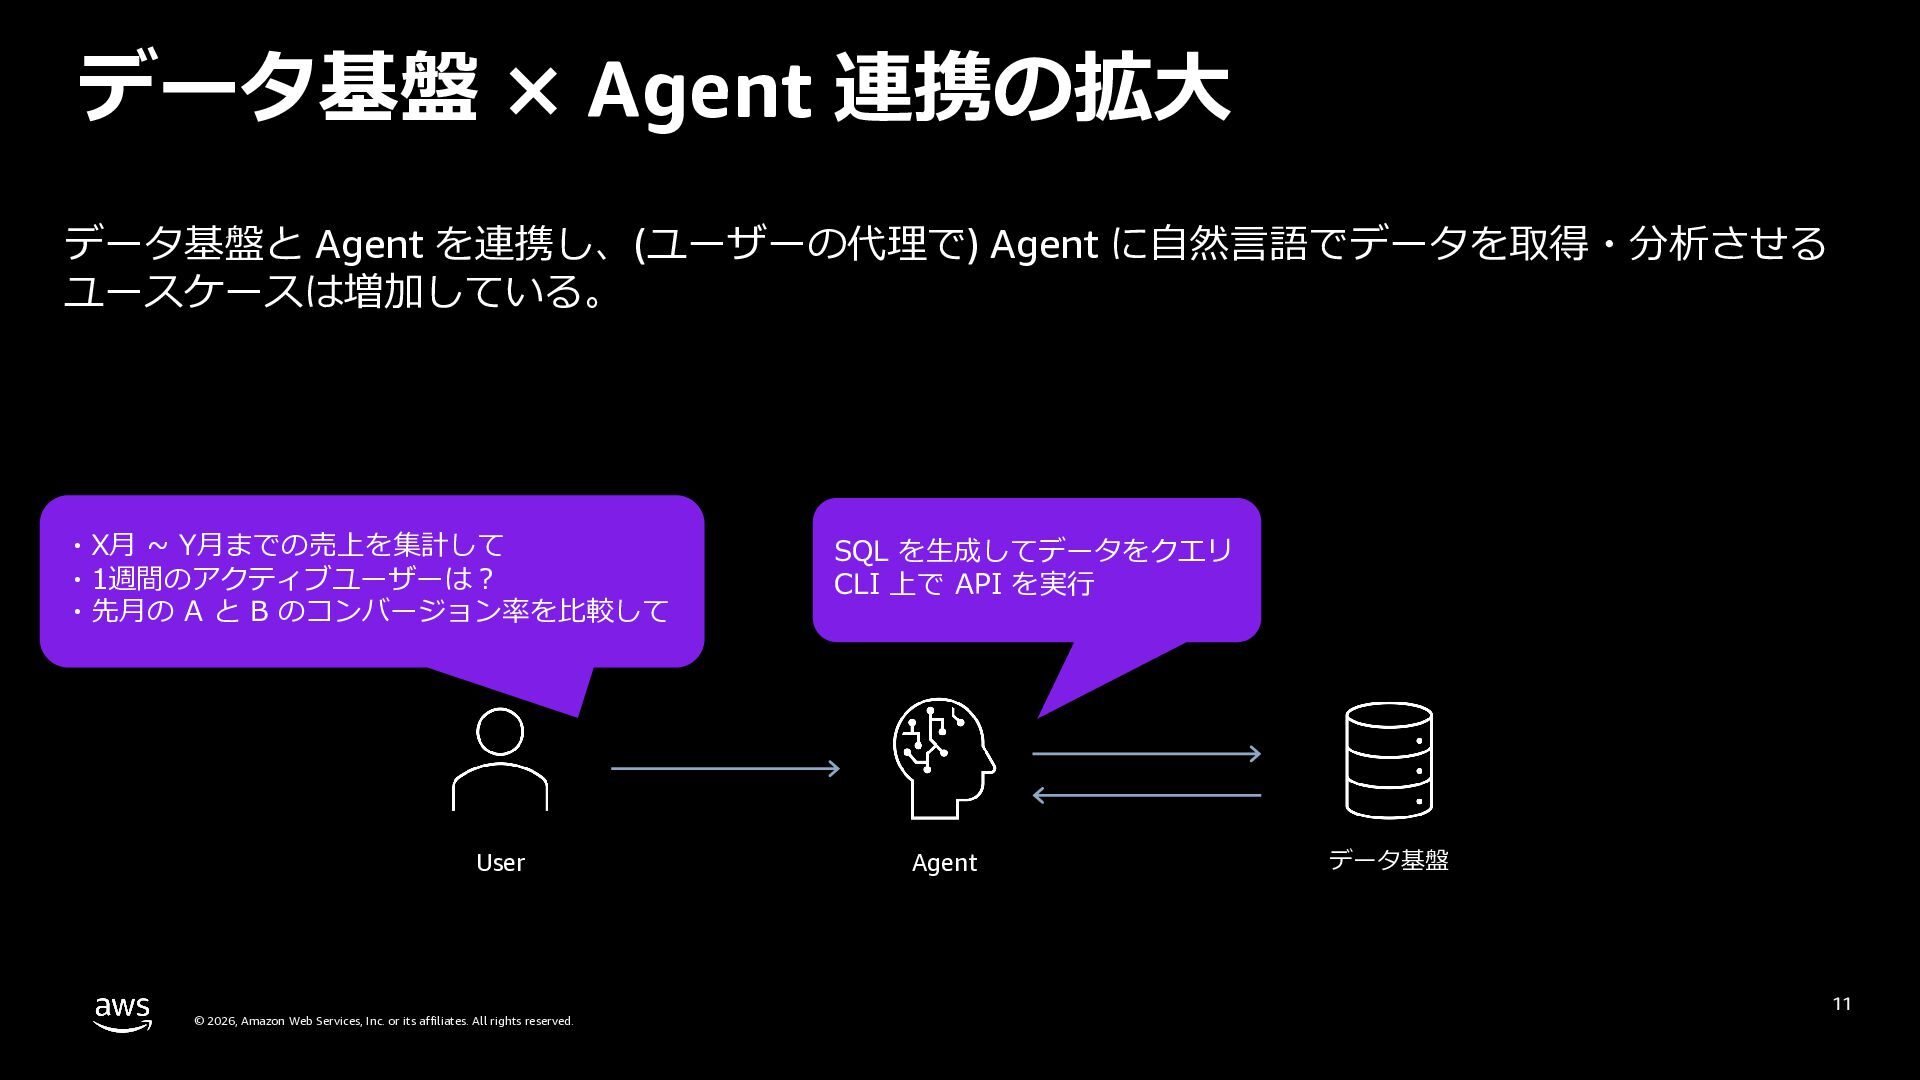
データ基盤 × Agent 連携の拡⼤ データ基盤と Agent を連携し、(ユーザーの代理で) Agent に⾃然⾔語でデータを取得・分析させる ユースケースは増加している。
・X⽉ ~ Y⽉までの売上を集計して ・1週間のアクティブユーザーは︖ ・先⽉の A と B のコンバージョン率を⽐較して User © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. SQL を⽣成してデータをクエリ CLI 上で API を実⾏ Agent データ基盤 11 -
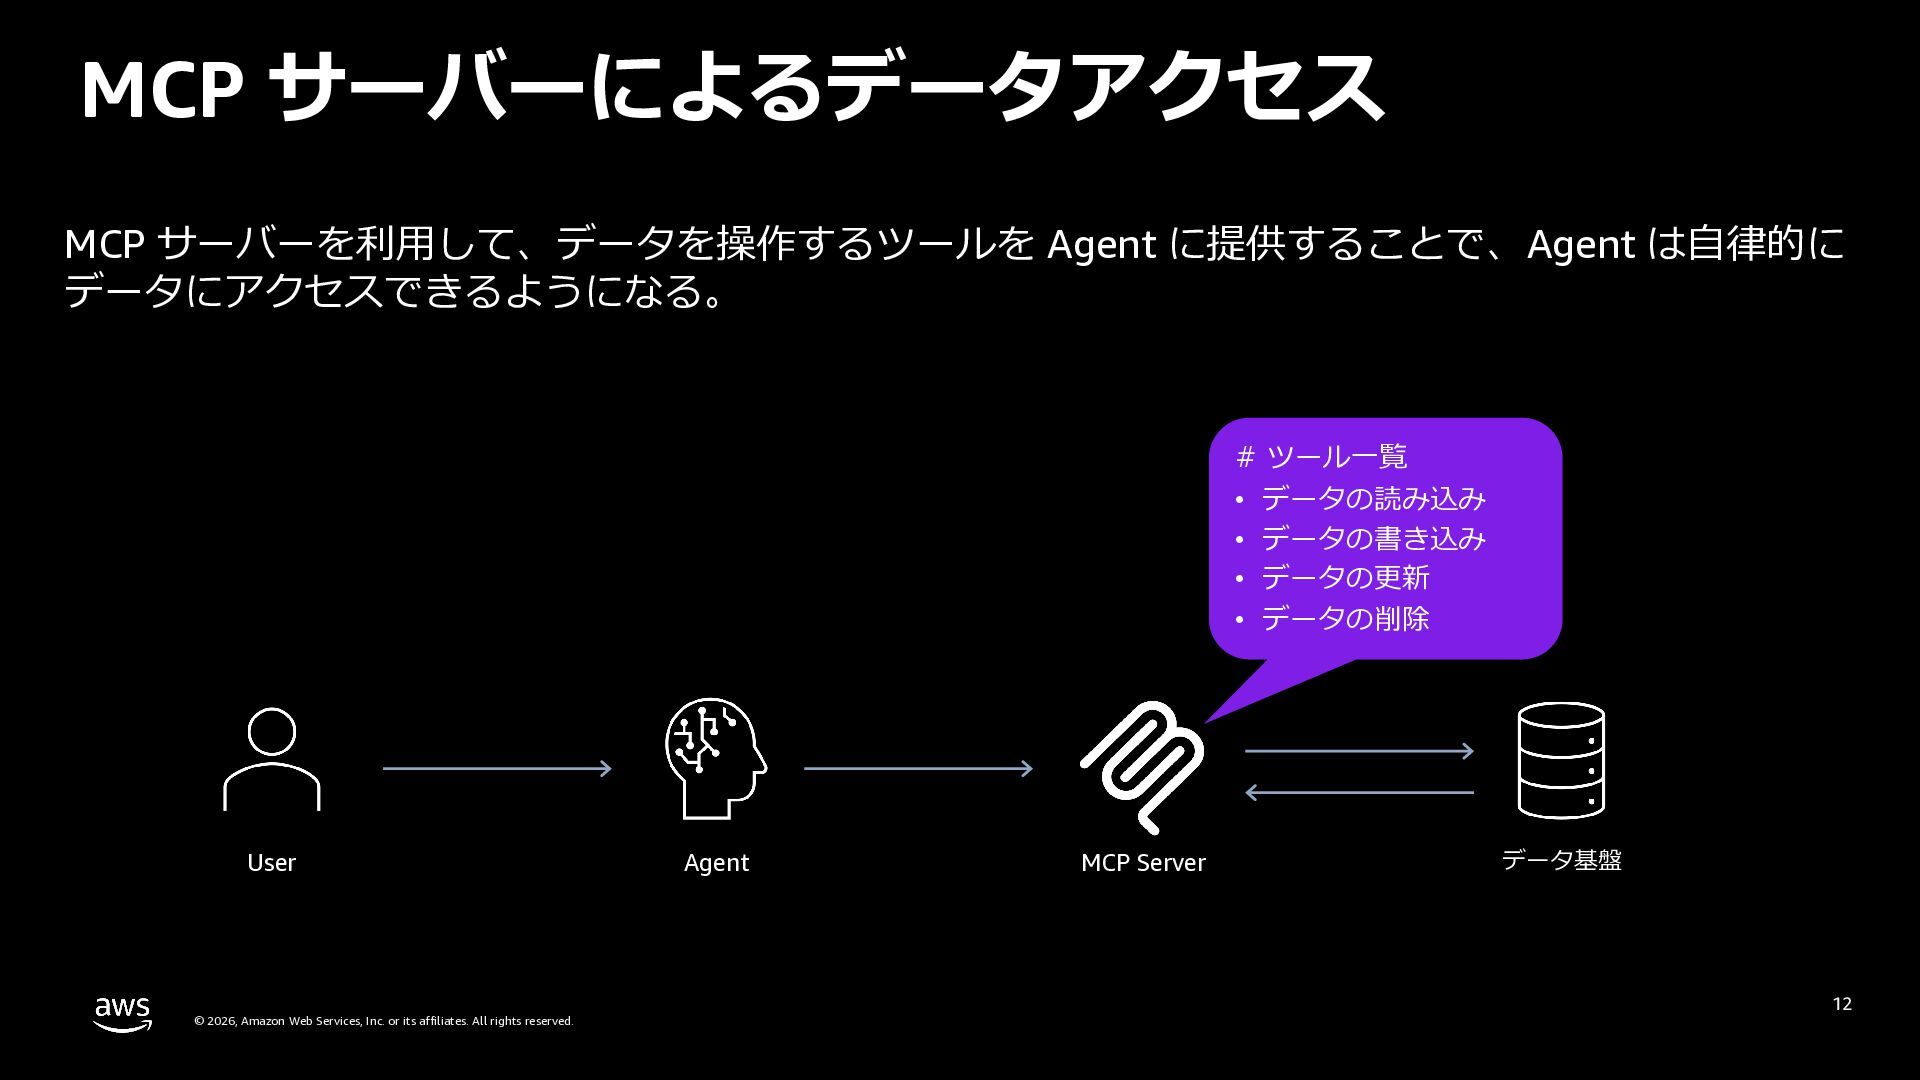
MCP サーバーによるデータアクセス MCP サーバーを利⽤して、データを操作するツールを Agent に提供することで、Agent は⾃律的に データにアクセスできるようになる。 # ツール⼀覧
• データの読み込み • データの書き込み • データの更新 • データの削除 User © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Agent MCP Server データ基盤 12 -
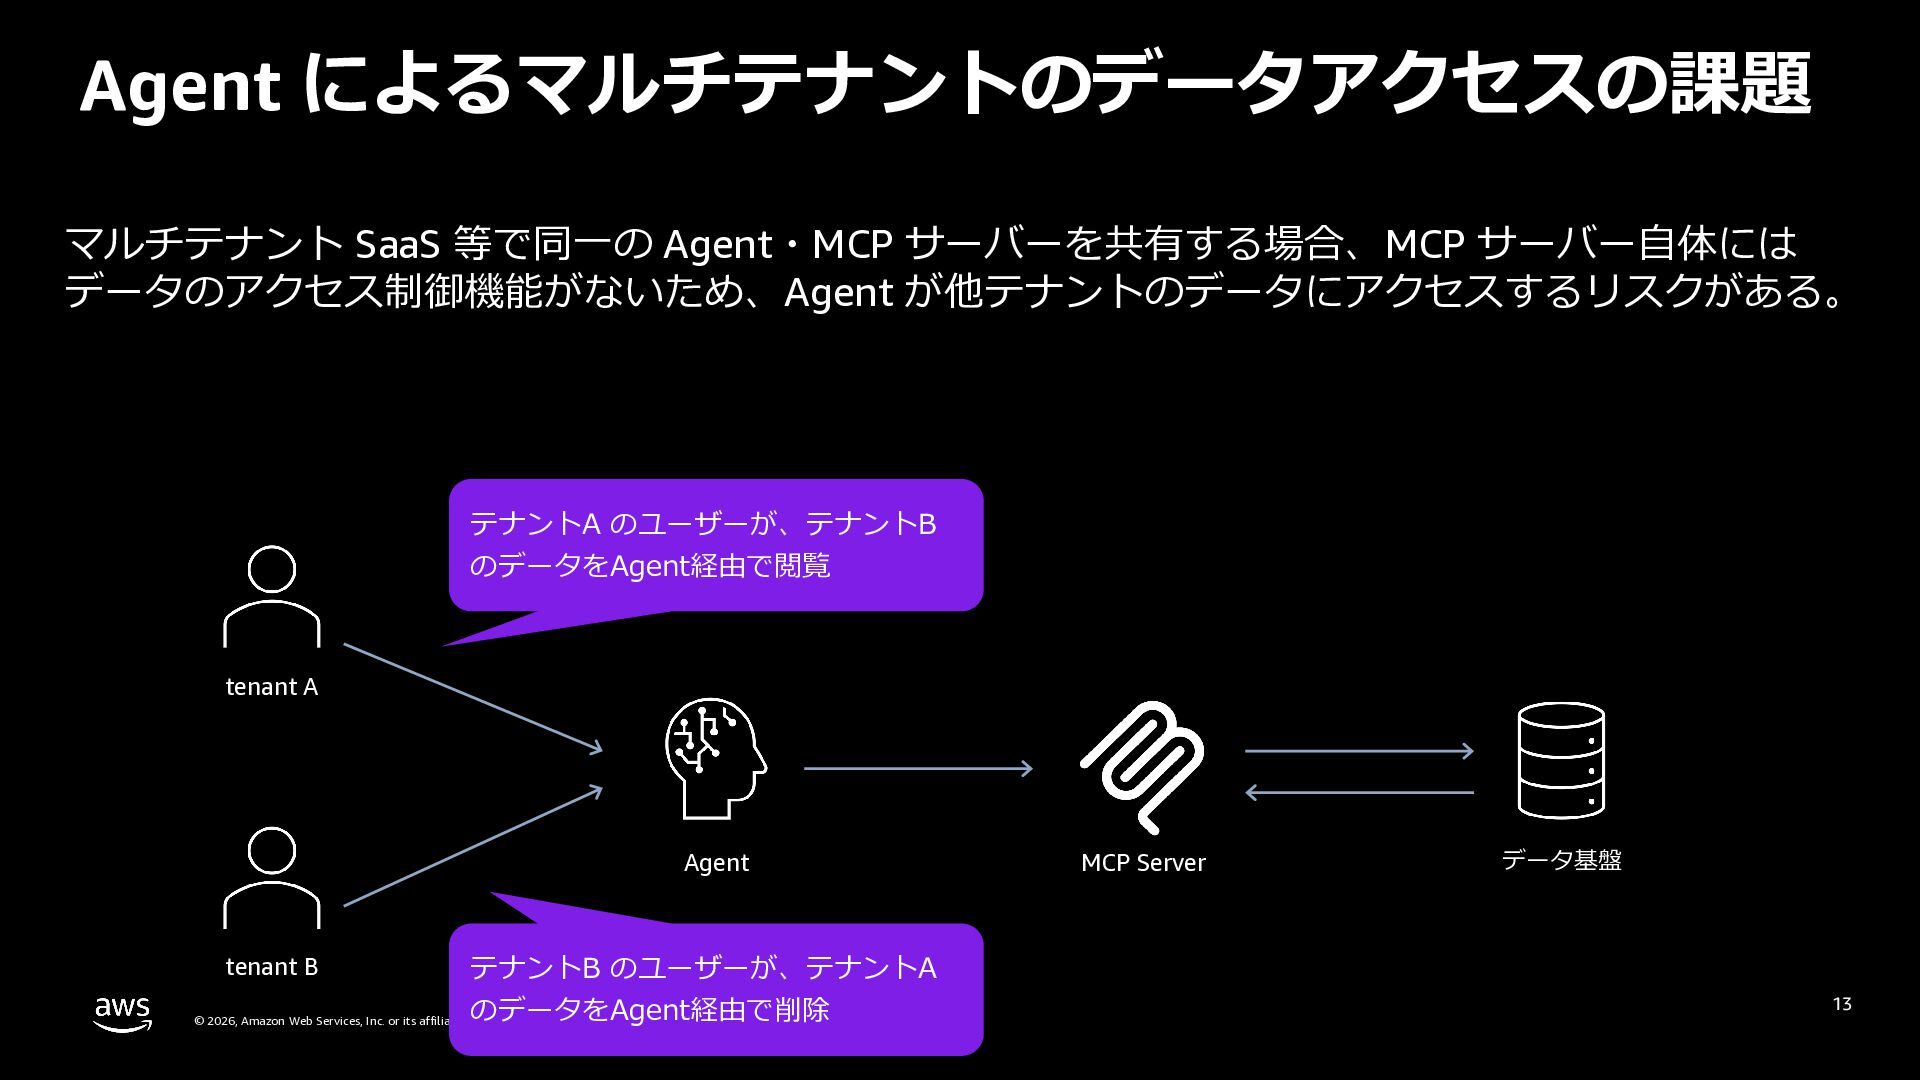
Agent によるマルチテナントのデータアクセスの課題 マルチテナント SaaS 等で同⼀の Agent・MCP サーバーを共有する場合、MCP サーバー⾃体には データのアクセス制御機能がないため、Agent が他テナントのデータにアクセスするリスクがある。
テナントA のユーザーが、テナントB のデータをAgent経由で閲覧 tenant A Agent テナントB のユーザーが、テナントA © 2026, Amazon Web Services, Inc. or its affiliates. のデータをAgent経由で削除 All rights reserved. MCP Server データ基盤 tenant B 13 -
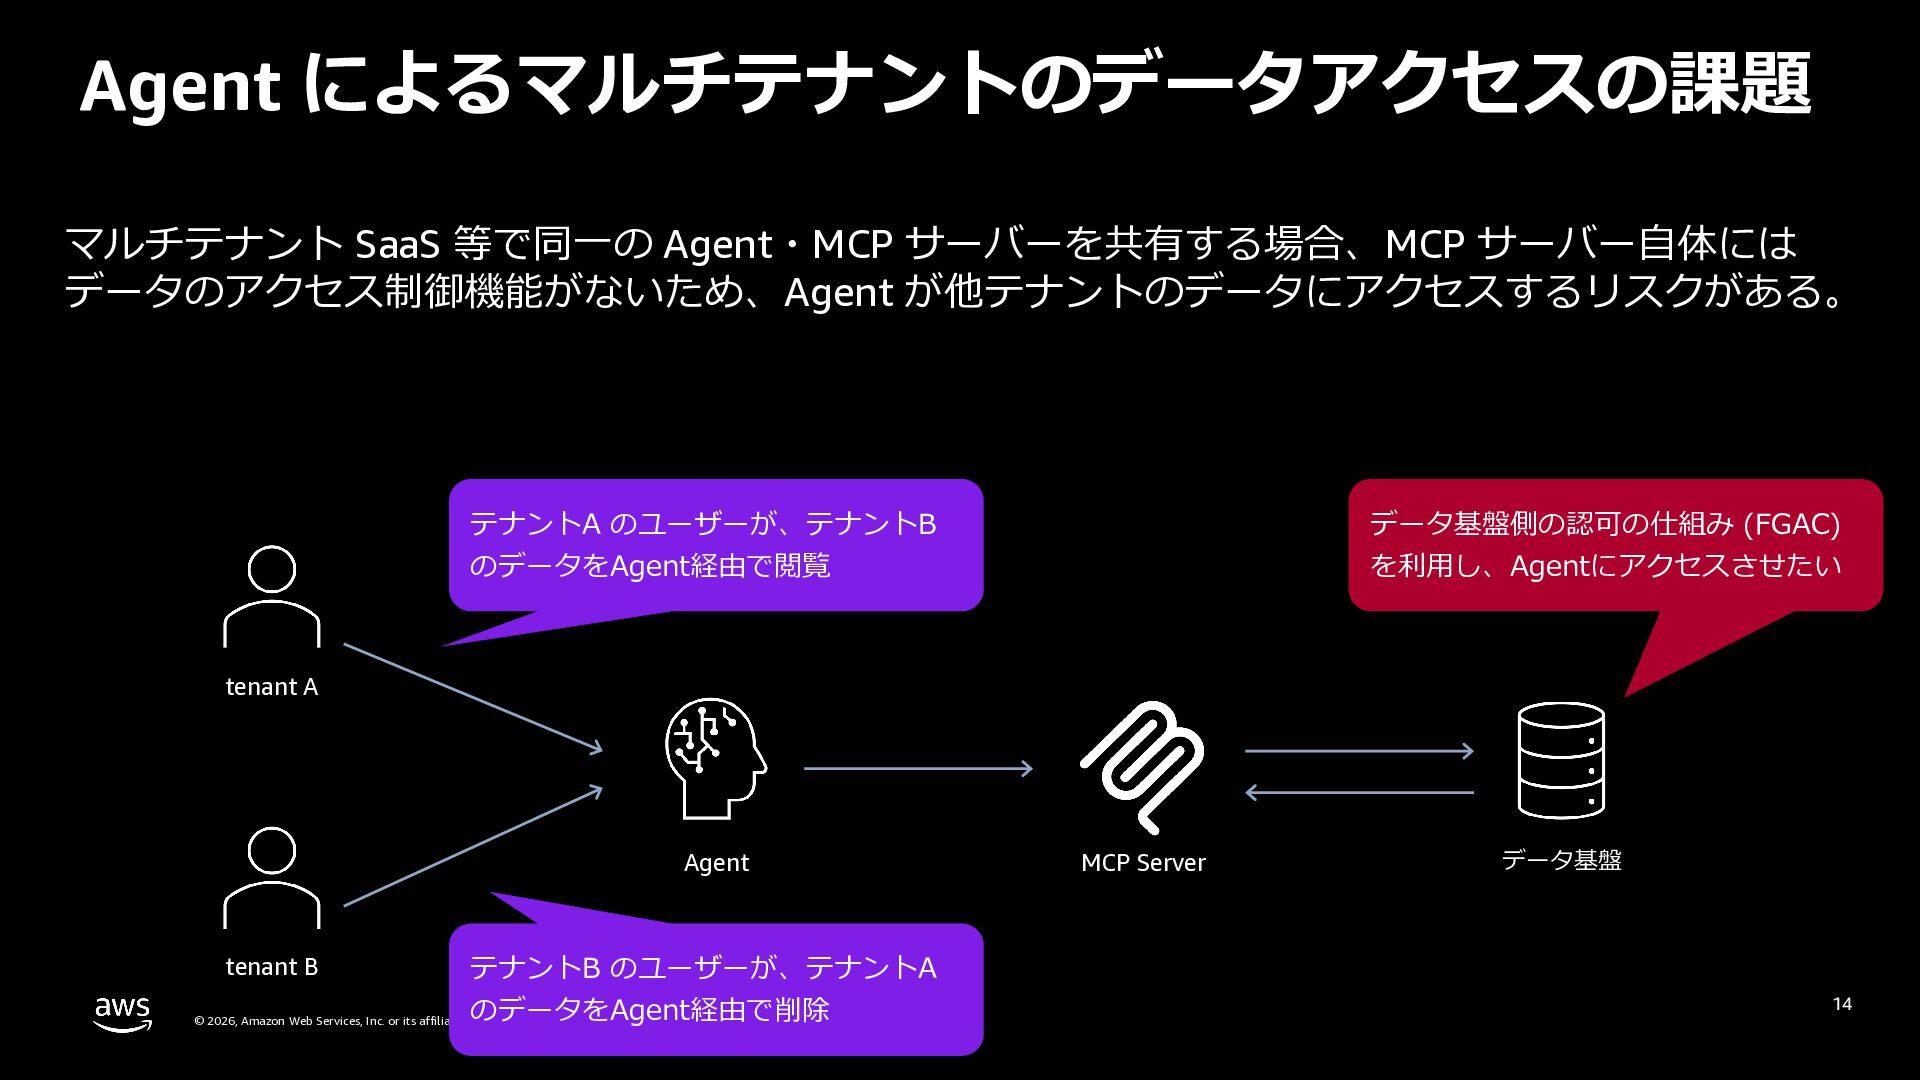
Agent によるマルチテナントのデータアクセスの課題 マルチテナント SaaS 等で同⼀の Agent・MCP サーバーを共有する場合、MCP サーバー⾃体には データのアクセス制御機能がないため、Agent が他テナントのデータにアクセスするリスクがある。
テナントA のユーザーが、テナントB のデータをAgent経由で閲覧 データ基盤側の認可の仕組み (FGAC) を利⽤し、Agentにアクセスさせたい tenant A Agent テナントB のユーザーが、テナントA © 2026, Amazon Web Services, Inc. or its affiliates. のデータをAgent経由で削除 All rights reserved. MCP Server データ基盤 tenant B 14 -
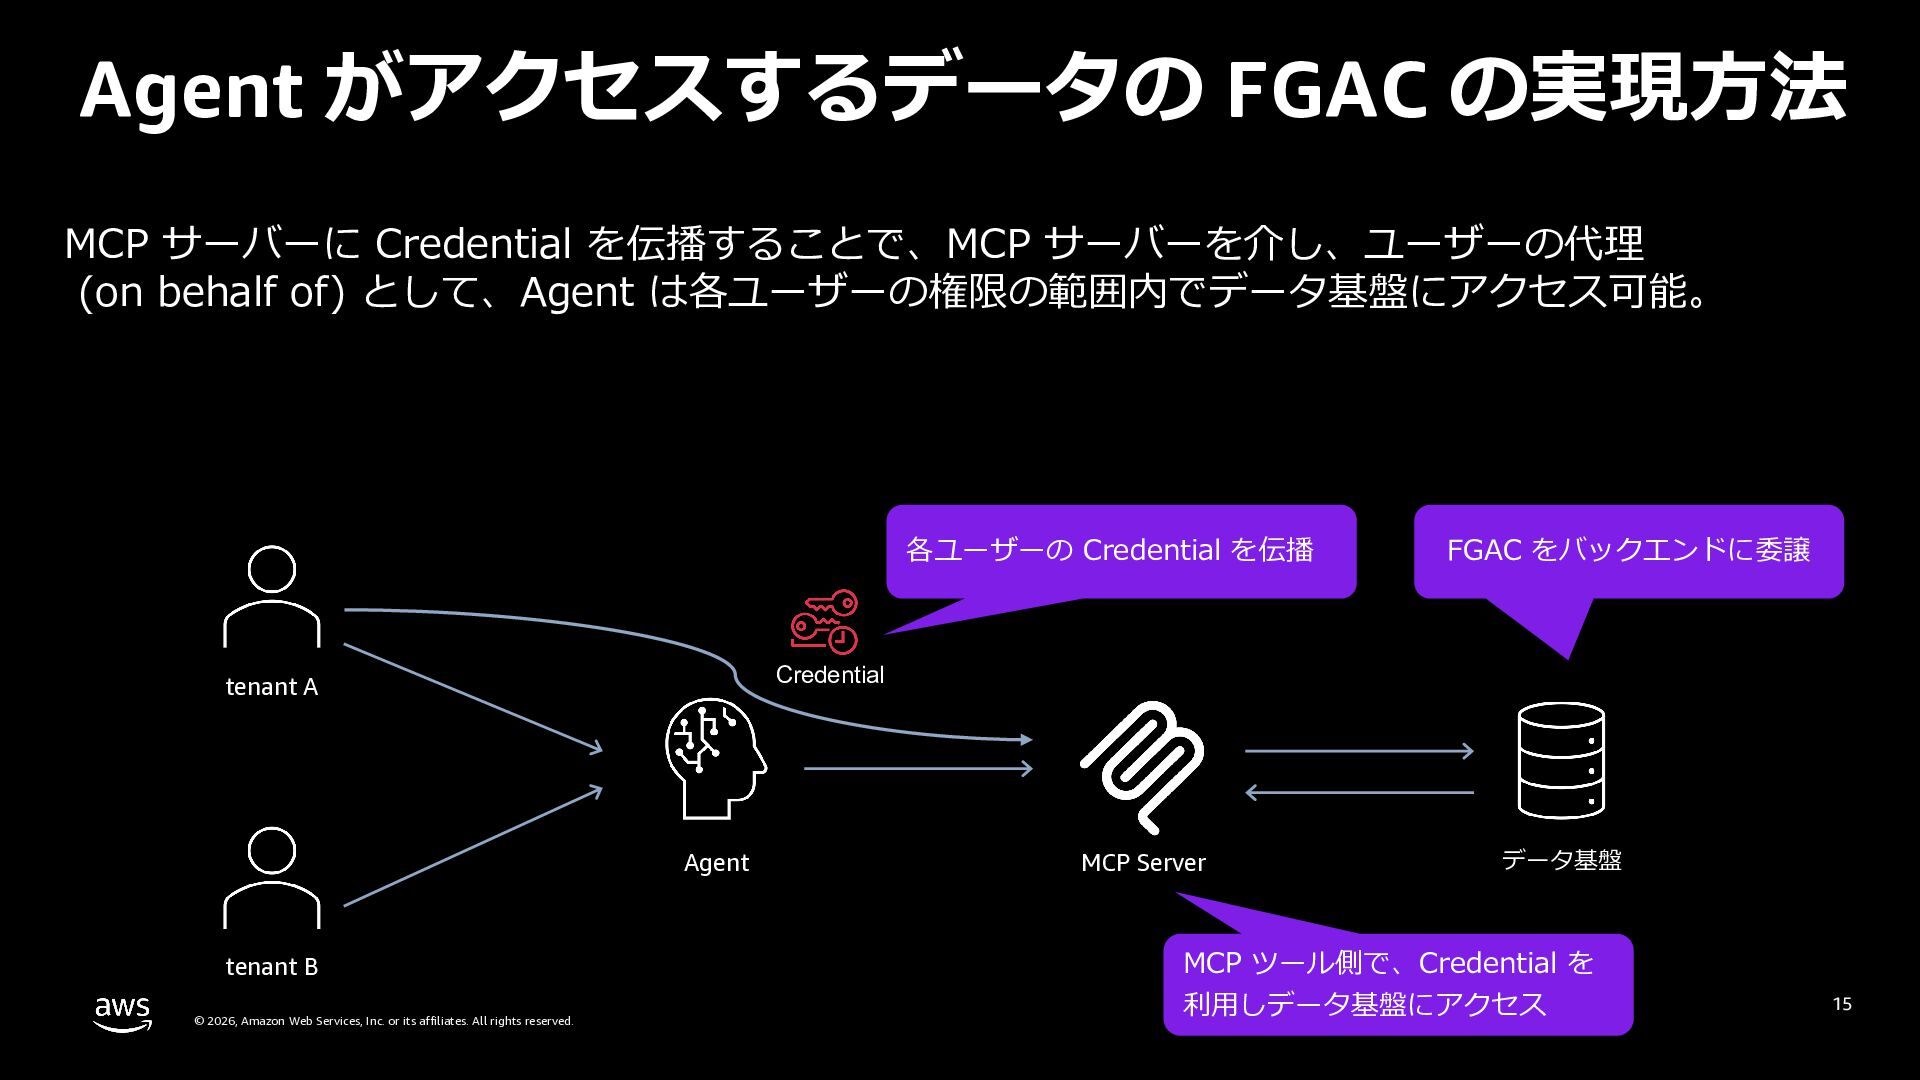
Agent がアクセスするデータの FGAC の実現⽅法 MCP サーバーに最⼩権限の Credential を伝播することで、ユーザーの代理 (on behalf
of) として、 Agent は各ユーザーの権限の範囲内で MCP サーバーを経由してデータ基盤にアクセス可能。 各ユーザーの Credential を伝播 Credential tenant A Agent tenant B © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. FGAC をバックエンドに委譲 MCP Server データ基盤 MCP ツール側で、Credential を 利⽤しデータ基盤にアクセス 15 -
AgentCore におけるデータの FGAC の実現⽅法 AgentCore Gateway では、MCP Server / Tools
に対し、最⼩権限の IAM Credential の伝播や、 OAuth の 3LO Access / On-Behalf-Of Access による最⼩権限での代理アクセスが可能。 AWS リソース以外への ユーザー代理アクセス (OAuth) AWS リソースへのアクセス (IAM) Agent AgentCore Gateway MCP Server Amazon Aurora Lambda Interceptors で 最⼩権限の IAM Credential に交換し伝播 Agent AgentCore Gateway MCP Server 3rd partyの リソース • ユーザーの同意を得て最⼩限のスコープのトークンを発⾏ • User Identity を保持しつつ、スコープを縮⼩したトークンに交換 3LO Access IAM (SigV4) © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. (Authorization Code Grant) ※初回のみユーザー同意が必要 On-Behalf-Of Access (Token Exchange / JWT Bearer Grant) ※認可サーバーが対応している必要がある 16 -
AgentCore におけるデータの FGAC の実現⽅法 AgentCore Gateway では、MCP Server / Tools
に対し、最⼩権限の IAM Credential の伝播や、 OAuth の 3LO Access / On-Behalf-Of Access による最⼩権限での代理アクセスが可能。 AWS リソース以外への ユーザー代理アクセス (OAuth) AWS リソースへのアクセス (IAM) Agent AgentCore Gateway MCP Server Amazon Aurora Lambda Interceptors で 最⼩権限の IAM Credential に交換し伝播 Agent AgentCore Gateway MCP Server 3rd partyの リソース • ユーザーの同意を得て最⼩限のスコープのトークンを発⾏ • マネージドにスコープを縮⼩したトークンに交換 3LO Access IAM (SigV4) 本発表ではこのパターンを解説します。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. (Authorization Code Grant) ※初回のみユーザー同意が必要 On-Behalf-Of Access (Token Exchange / JWT Bearer Grant) ※認可サーバーが対応している必要がある 17 -
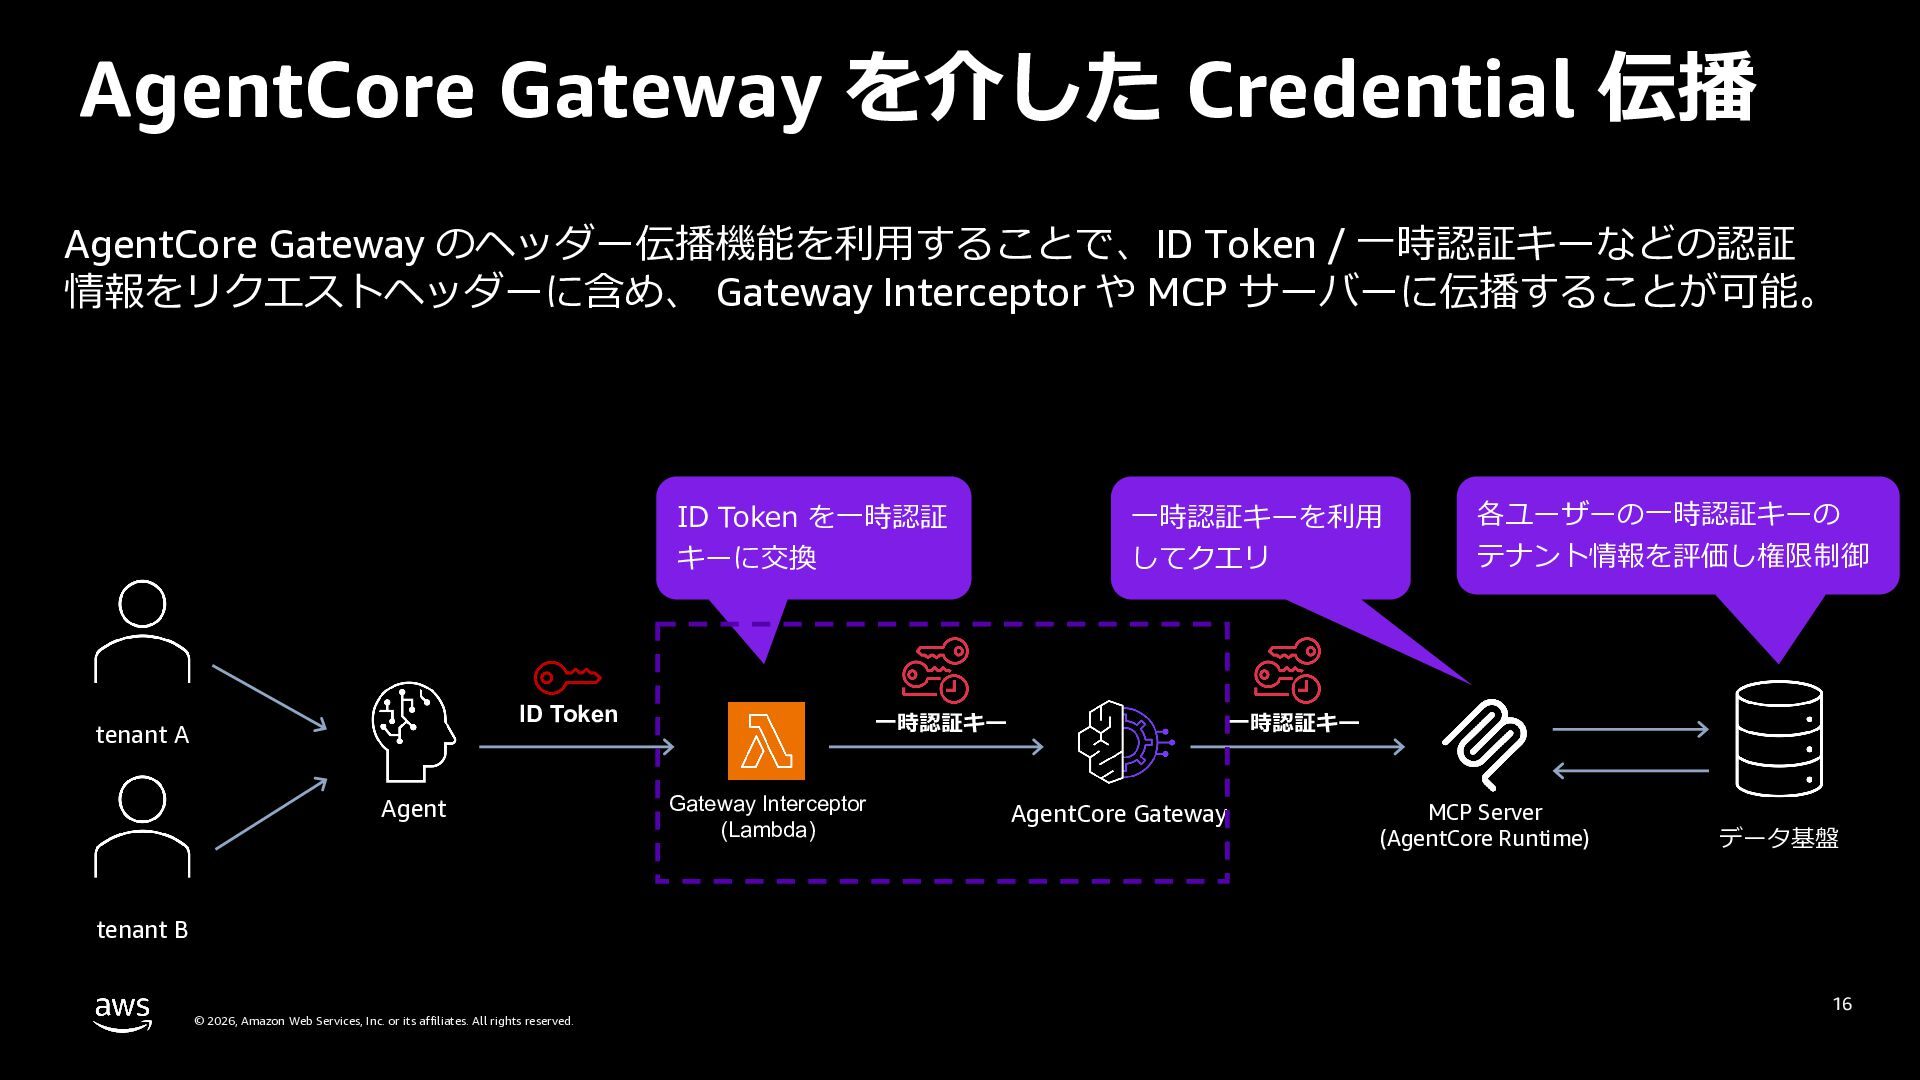
AgentCore Gateway を介した Credential 伝播 AgentCore Gateway のヘッダー伝播機能を利⽤することで、ID Token /
⼀時認証キーなどの認証 情報をリクエストヘッダーに含め、 Gateway Interceptor や MCP サーバーに伝播することが可能。 ID Token を⼀時認証 キーに交換 ID Token tenant A Agent ⼀時認証キーを利⽤ してクエリ ⼀時認証キー Gateway Interceptor (Lambda) 各ユーザーの⼀時認証キーの テナント情報を評価し権限制御 ⼀時認証キー AgentCore Gateway MCP Server (AgentCore Runtime) データ基盤 tenant B © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 18 -
AgentCore Gateway の前提知識 © 2026, Amazon Web Services, Inc. or
its affiliates. All rights reserved. 19 -
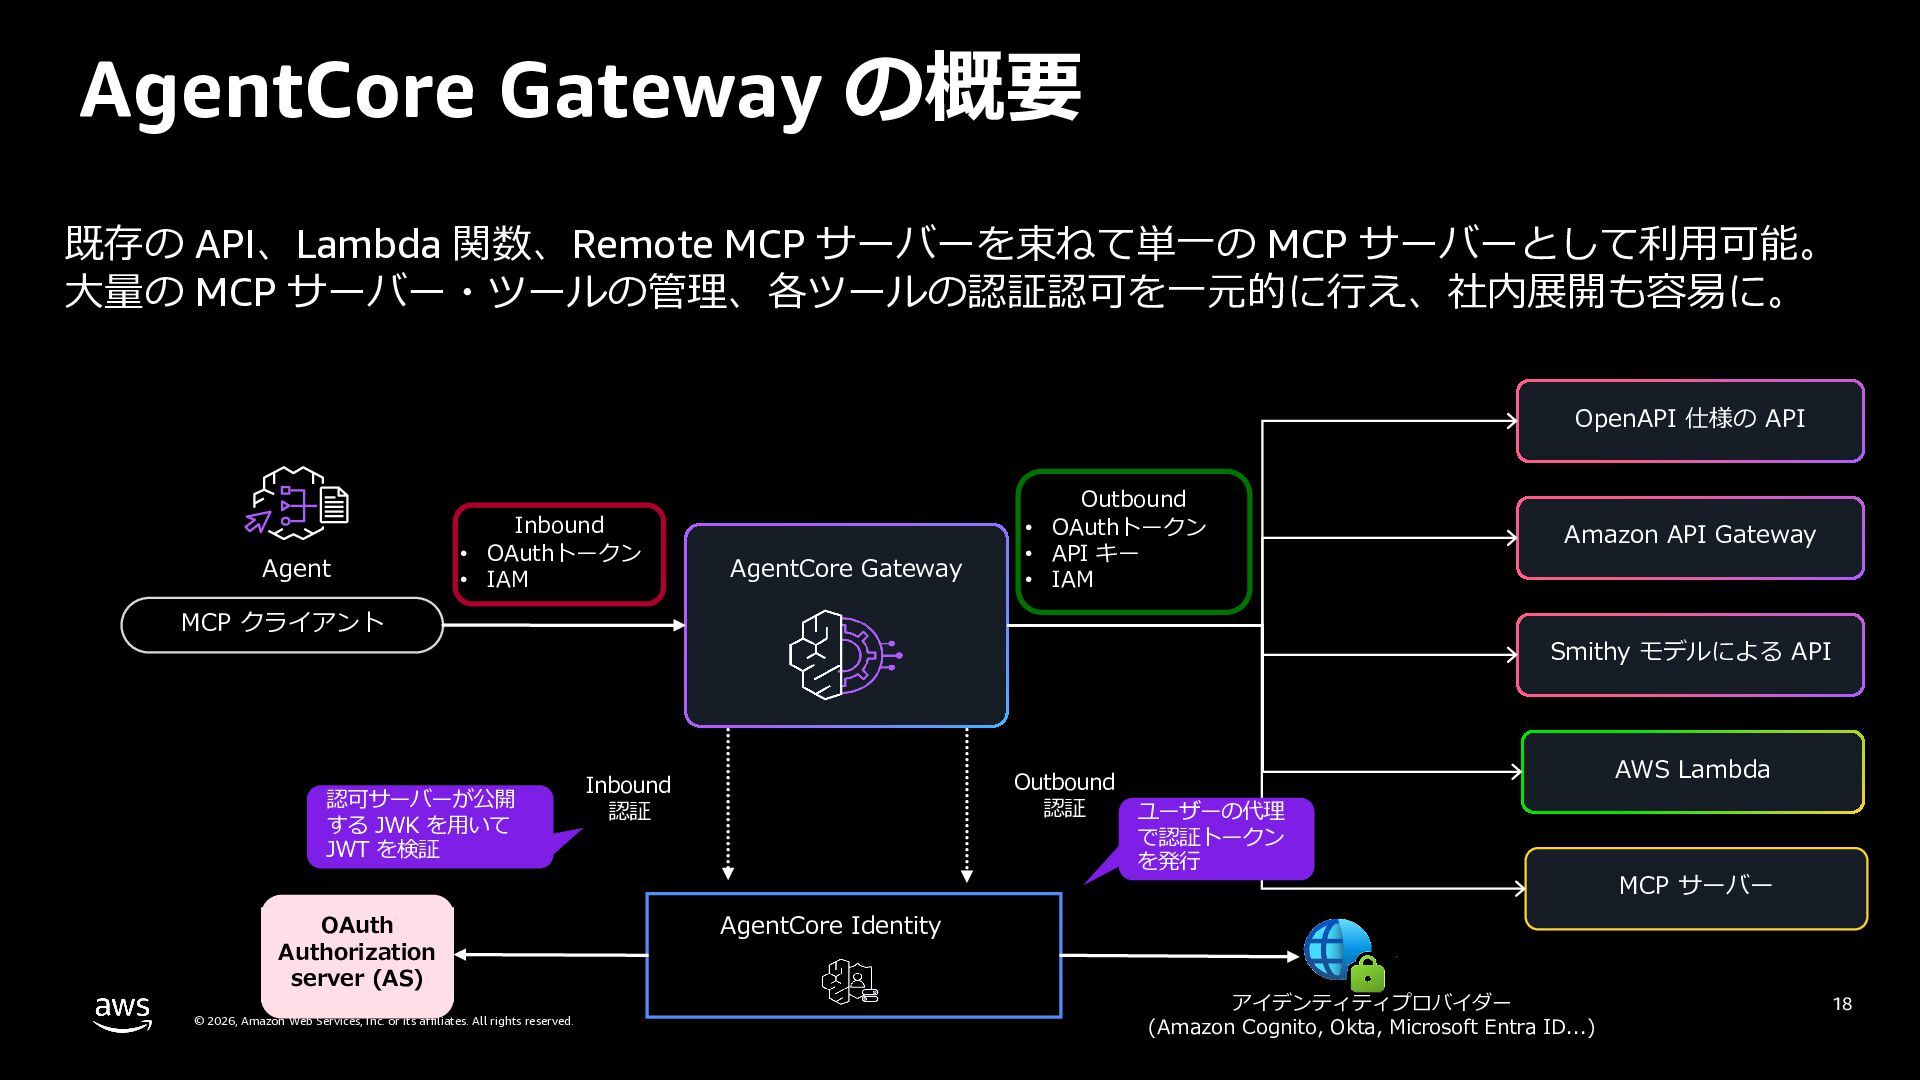
AgentCore Gateway の概要 既存の API、Lambda 関数、Remote MCP サーバーを束ねて単⼀の MCP サーバーとして利⽤可能。
⼤量の MCP サーバー・ツールの管理、各ツールの認証認可を⼀元的に⾏え、社内展開も容易に。 OpenAPI 仕様の API Agent Inbound • OAuthトークン • IAM AgentCore Gateway Outbound • OAuthトークン • API キー • IAM MCP クライアント 認可サーバーが公開 する JWK を⽤いて JWT を検証 OAuth Authorization server (AS) © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Amazon API Gateway Smithy モデルによる API Outbound 認証 ユーザーの代理 で認証トークン を発⾏ Inbound 認証 AWS Lambda MCP サーバー AgentCore Identity アイデンティティプロバイダー (Amazon Cognito, Okta, Microsoft Entra ID...) 20 -
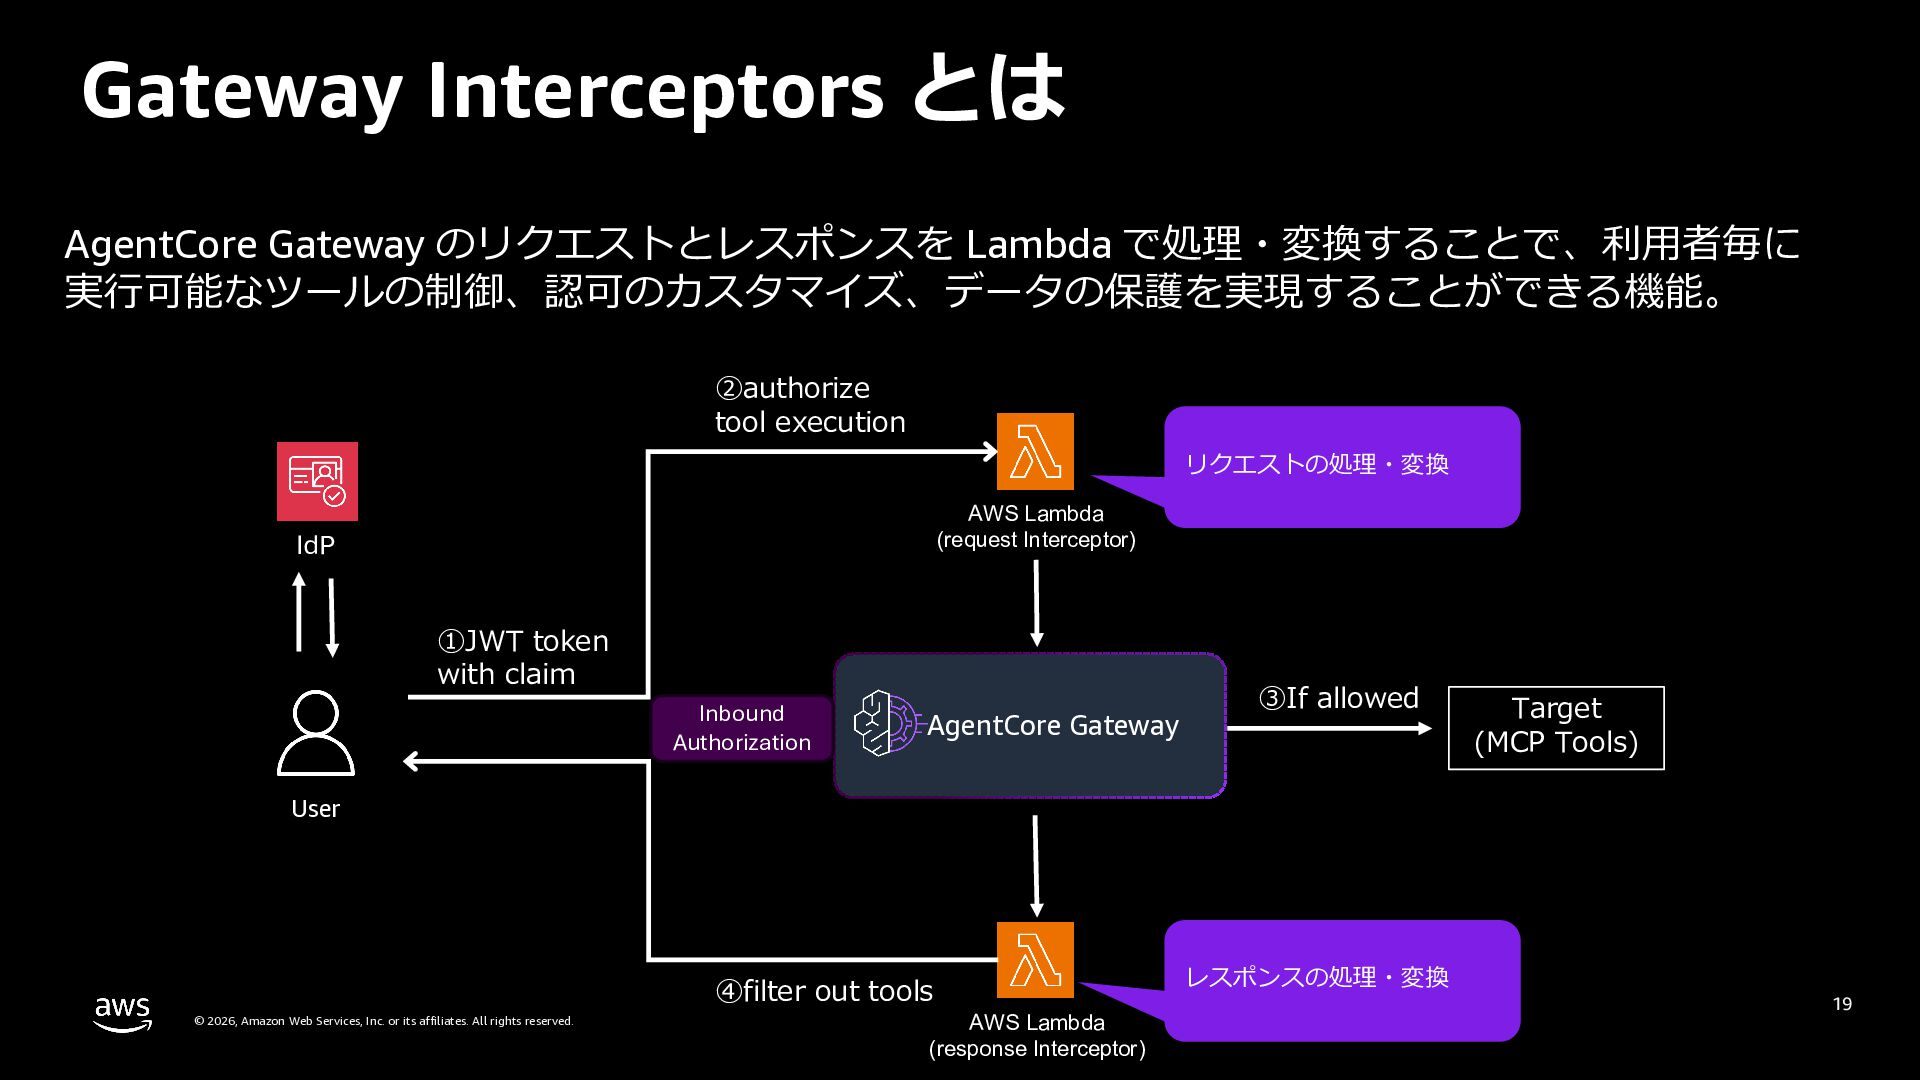
Gateway Interceptors とは AgentCore Gateway のリクエストとレスポンスを Lambda で処理・変換することで、利⽤者毎に 実⾏可能なツールの制御、認可のカスタマイズ、データの保護を実現することができる機能。 ②authorize
tool execution リクエストの処理・変換 AWS Lambda (request Interceptor) IdP ①JWT token with claim Inbound Authorization AgentCore Gateway ③If allowed Target (MCP Tools) User ④filter out tools © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AWS Lambda (response Interceptor) レスポンスの処理・変換 21 -
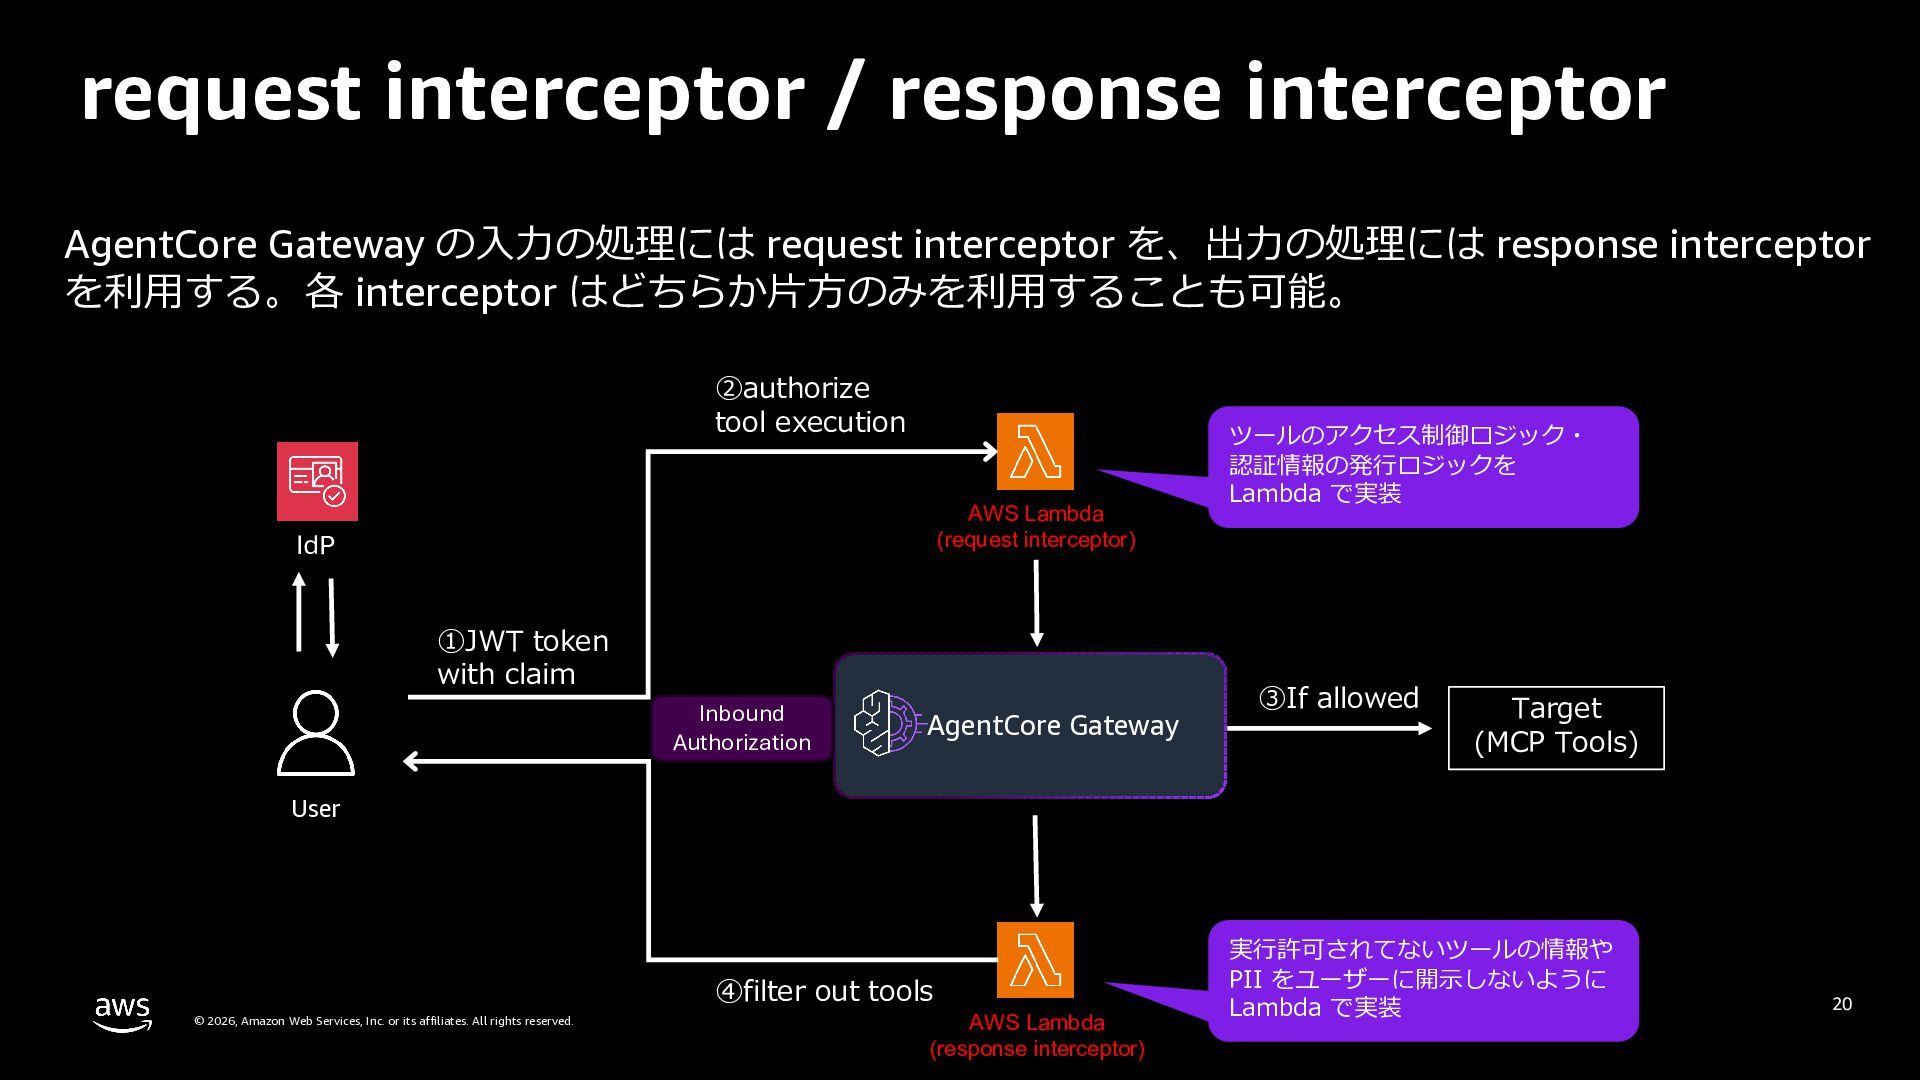
request interceptor / response interceptor AgentCore Gateway の⼊⼒の処理には request interceptor
を、出⼒の処理には response interceptor を利⽤する。各 interceptor はどちらか⽚⽅のみを利⽤することも可能。 ②authorize tool execution AWS Lambda (request interceptor) IdP ①JWT token with claim Inbound Authorization AgentCore Gateway ツールのアクセス制御ロジック・ 認証情報の発⾏ロジックを Lambda で実装 ③If allowed Target (MCP Tools) User ④filter out tools © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AWS Lambda (response interceptor) 実⾏許可されてないツールの情報や PII をユーザーに開⽰しないように Lambda で実装 22 -
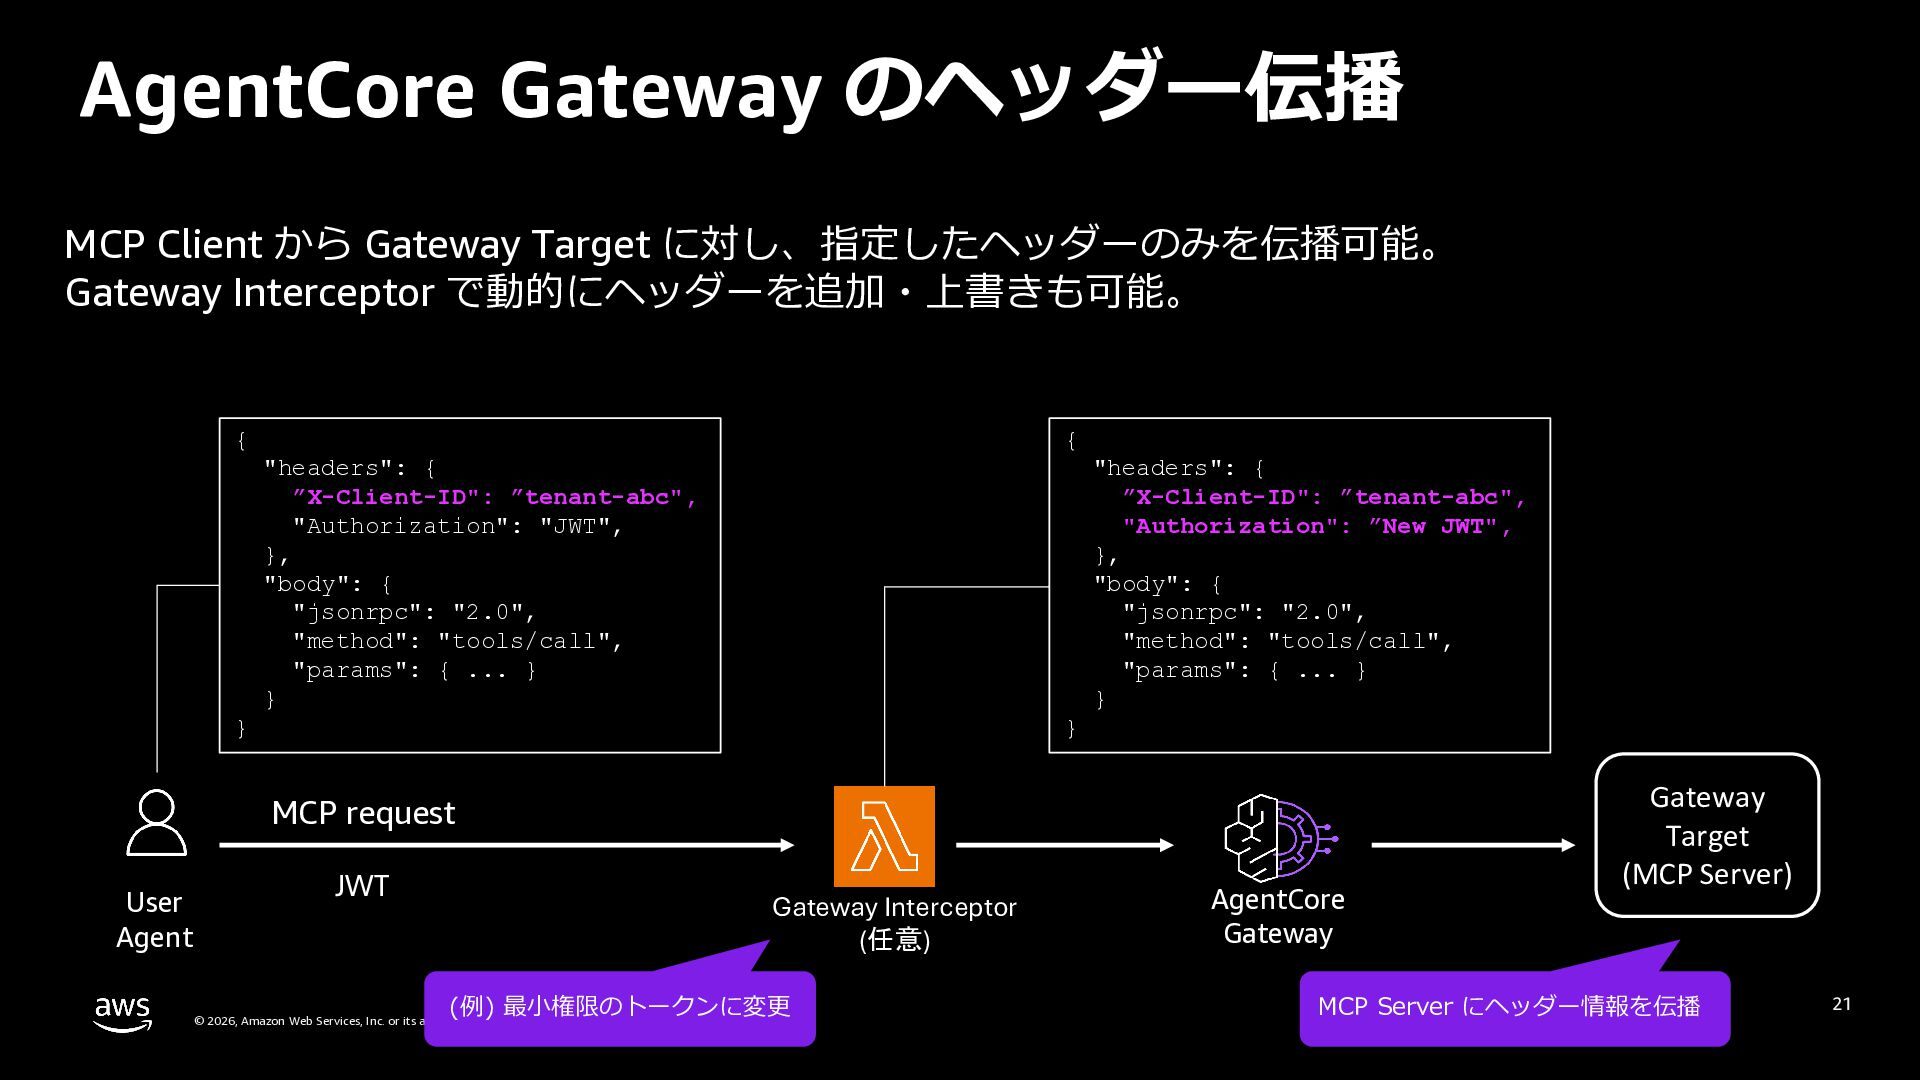
AgentCore Gateway のヘッダー伝播 MCP Client から Gateway Target に対し、指定したヘッダーのみを伝播可能。 Gateway
Interceptor で動的にヘッダーを追加・上書きも可能。 { { "headers": { ”X-Client-ID": ”tenant-abc", "Authorization": "JWT", }, "body": { "jsonrpc": "2.0", "method": "tools/call", "params": { ... } } "headers": { ”X-Client-ID": ”tenant-abc", "Authorization": ”New JWT", }, "body": { "jsonrpc": "2.0", "method": "tools/call", "params": { ... } } } } MCP request User Agent JWT Gateway Interceptor (任意) (例) 最⼩権限のトークンに変更 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AgentCore Gateway Gateway Target (MCP Server) MCP Server にヘッダー情報を伝播 23 -
AgentCore Gateway を利⽤した データ基盤の FGAC アーキテクチャ © 2026, Amazon Web
Services, Inc. or its affiliates. All rights reserved. 24 -
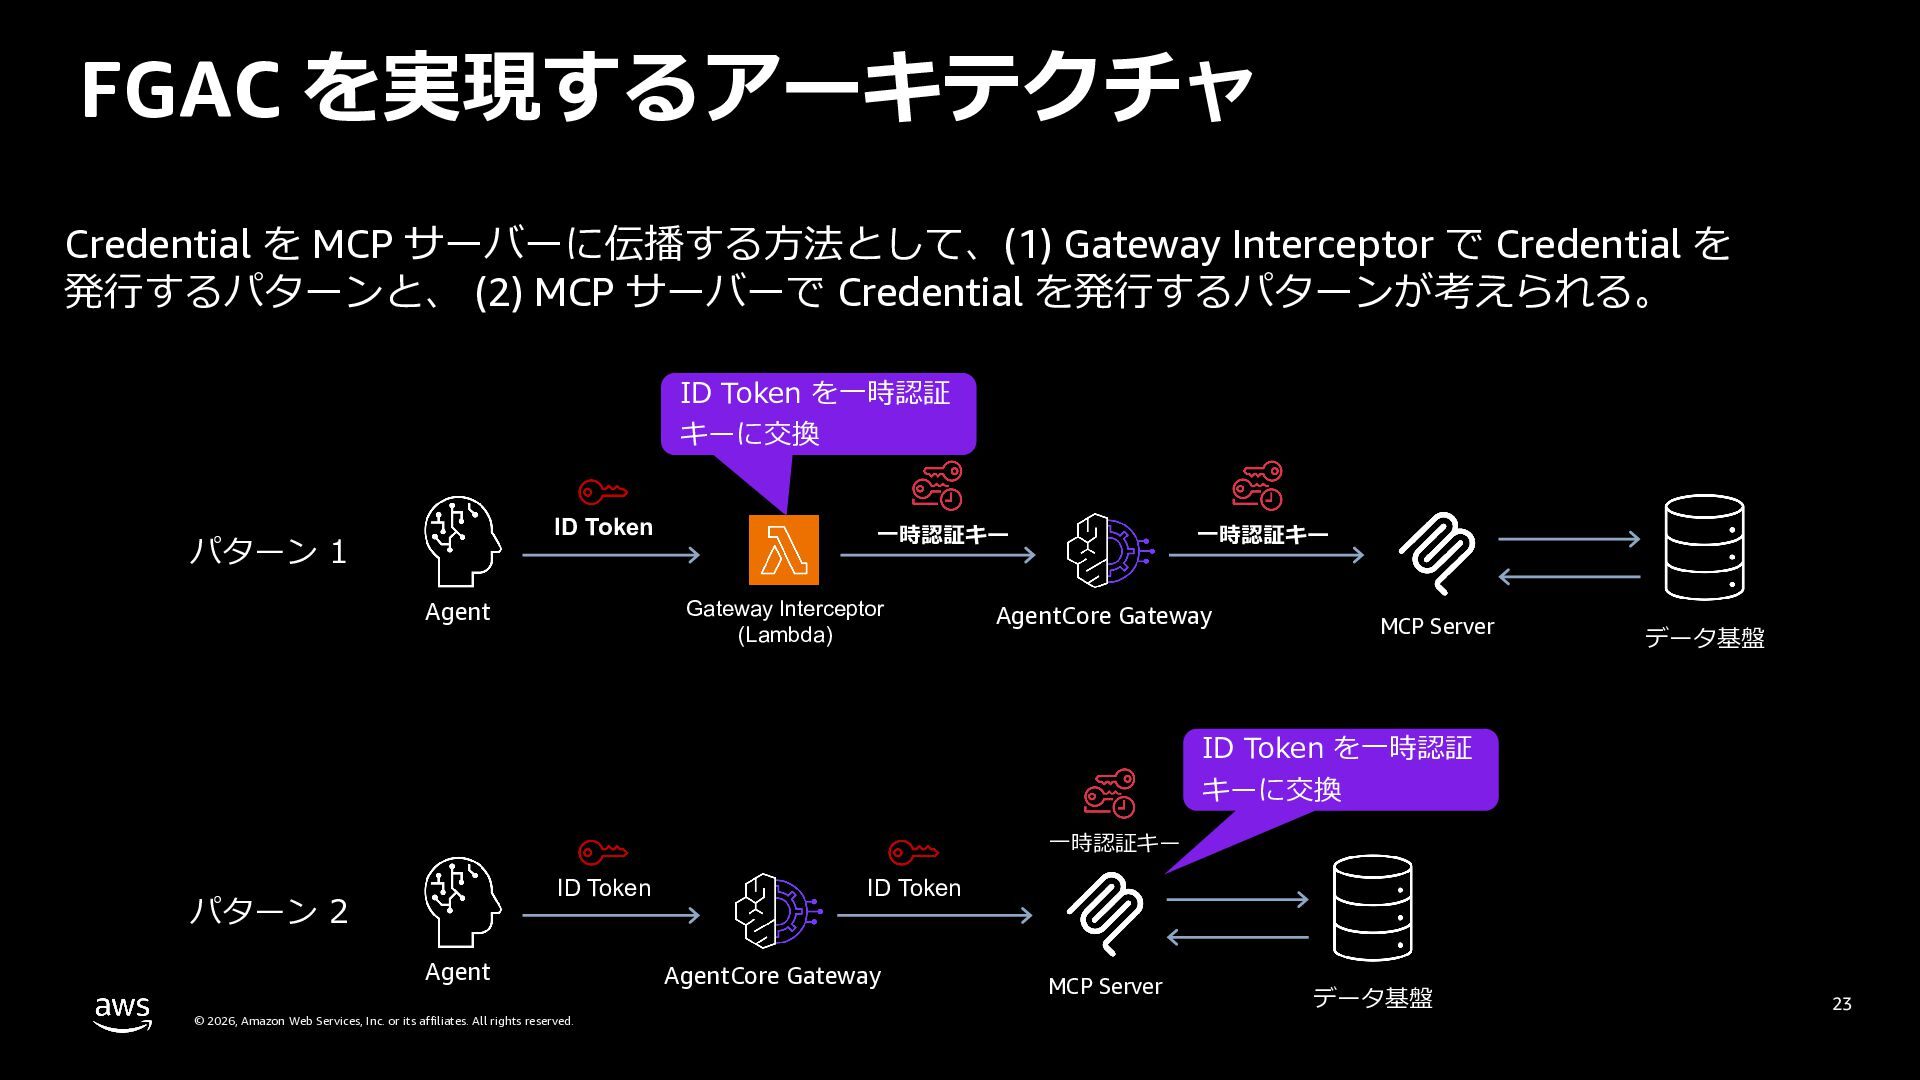
FGAC を実現するアーキテクチャ Credential を MCP サーバーに伝播する⽅法として、(1) Gateway Interceptor で Credential
を 発⾏するパターンと、 (2) MCP サーバーで Credential を発⾏するパターンが考えられる。 ID Token を⼀時認証 キーに交換 ID Token パターン 1 ⼀時認証キー Gateway Interceptor (Lambda) Agent ⼀時認証キー AgentCore Gateway MCP Server データ基盤 ID Token を⼀時認証 キーに交換 ⼀時認証キー ID Token パターン 2 Agent © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ID Token AgentCore Gateway MCP Server データ基盤 25 -
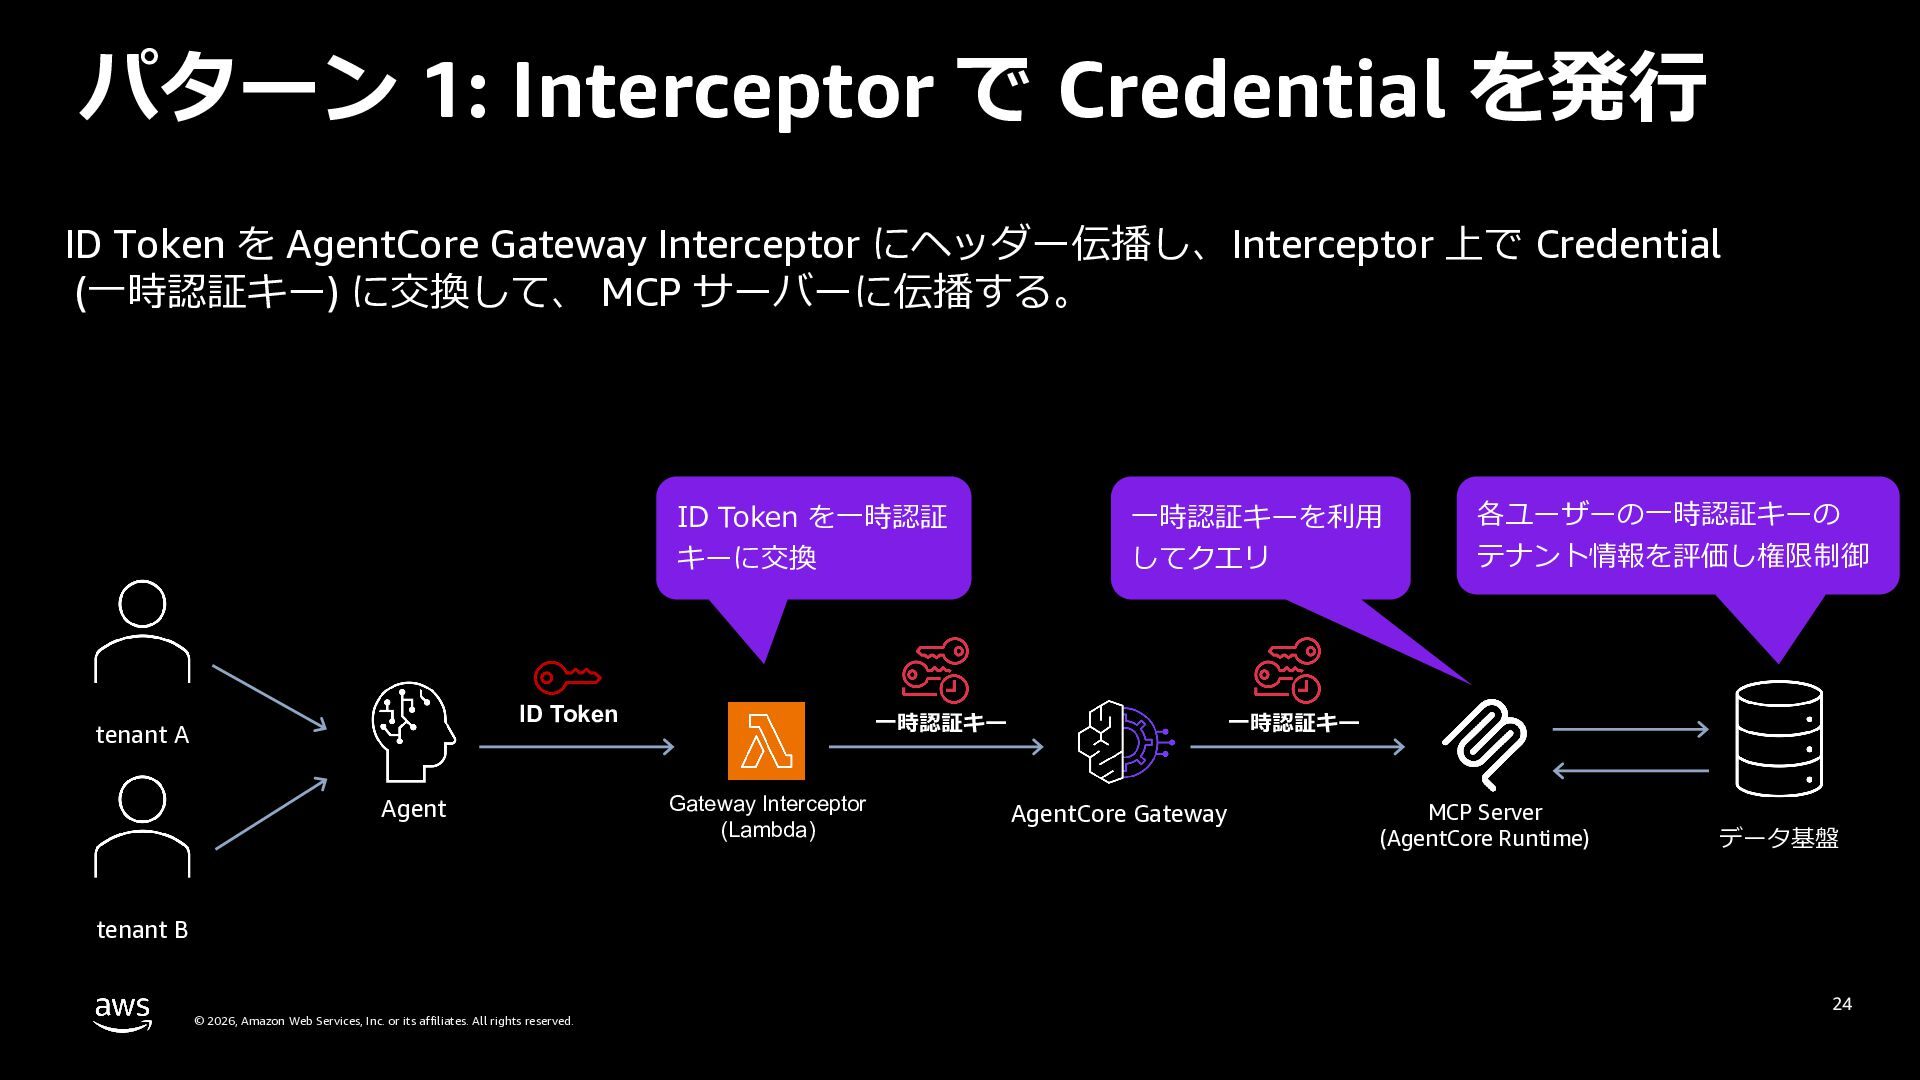
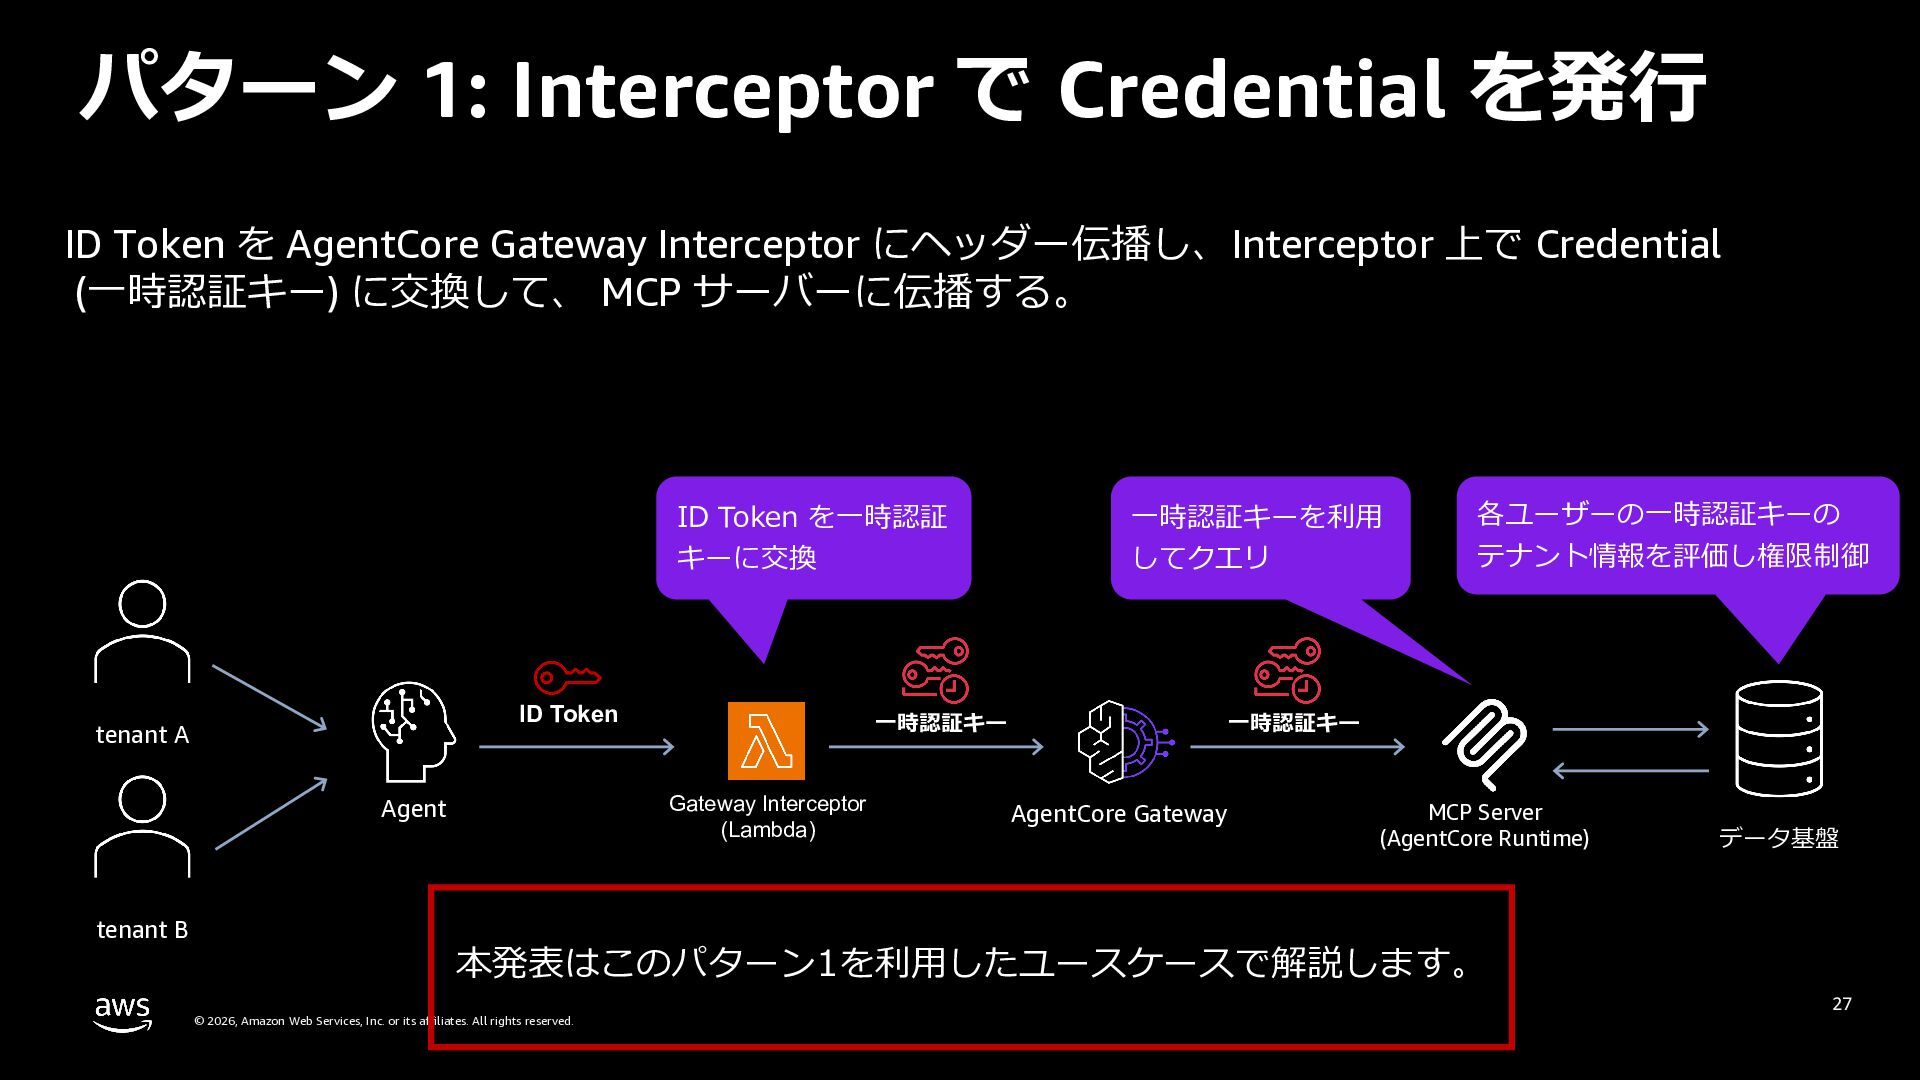
パターン 1: Interceptor で Credential を発⾏ ID Token を AgentCore
Gateway Interceptor にヘッダー伝播し、Interceptor 上で Credential (⼀時認証キー) に交換して、 MCP サーバーに伝播する。 ID Token を⼀時認証 キーに交換 ID Token tenant A Agent ⼀時認証キーを利⽤ してクエリ ⼀時認証キー Gateway Interceptor (Lambda) 各ユーザーの⼀時認証キーの テナント情報を評価し権限制御 ⼀時認証キー AgentCore Gateway MCP Server (AgentCore Runtime) データ基盤 tenant B © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 26 -
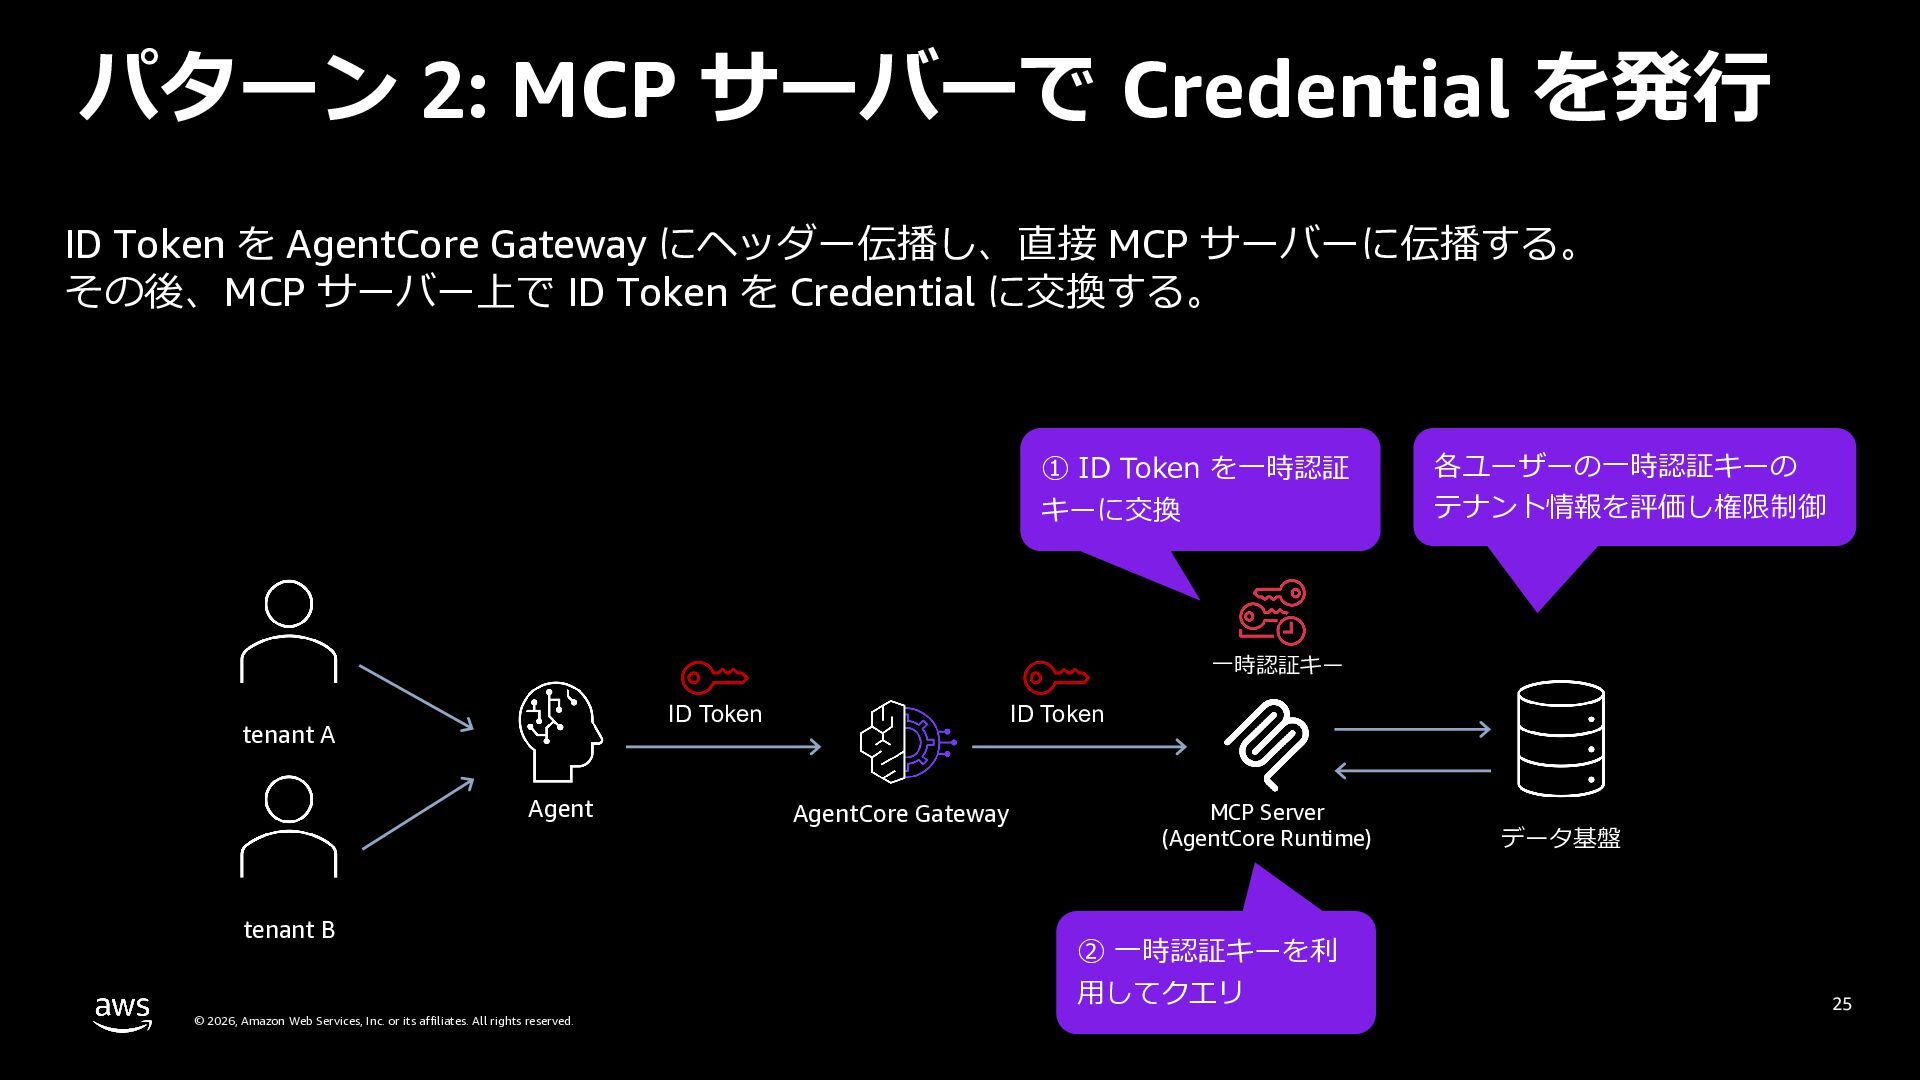
パターン 2: MCP サーバーで Credential を発⾏ ID Token を AgentCore
Gateway にヘッダー伝播し、直接 MCP サーバーに伝播する。 その後、MCP サーバー上で ID Token を Credential に交換する。 ① ID Token を⼀時認証 キーに交換 各ユーザーの⼀時認証キーの テナント情報を評価し権限制御 ⼀時認証キー ID Token tenant A Agent tenant B © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ID Token AgentCore Gateway MCP Server (AgentCore Runtime) データ基盤 ② ⼀時認証キーを利 ⽤してクエリ 27 -
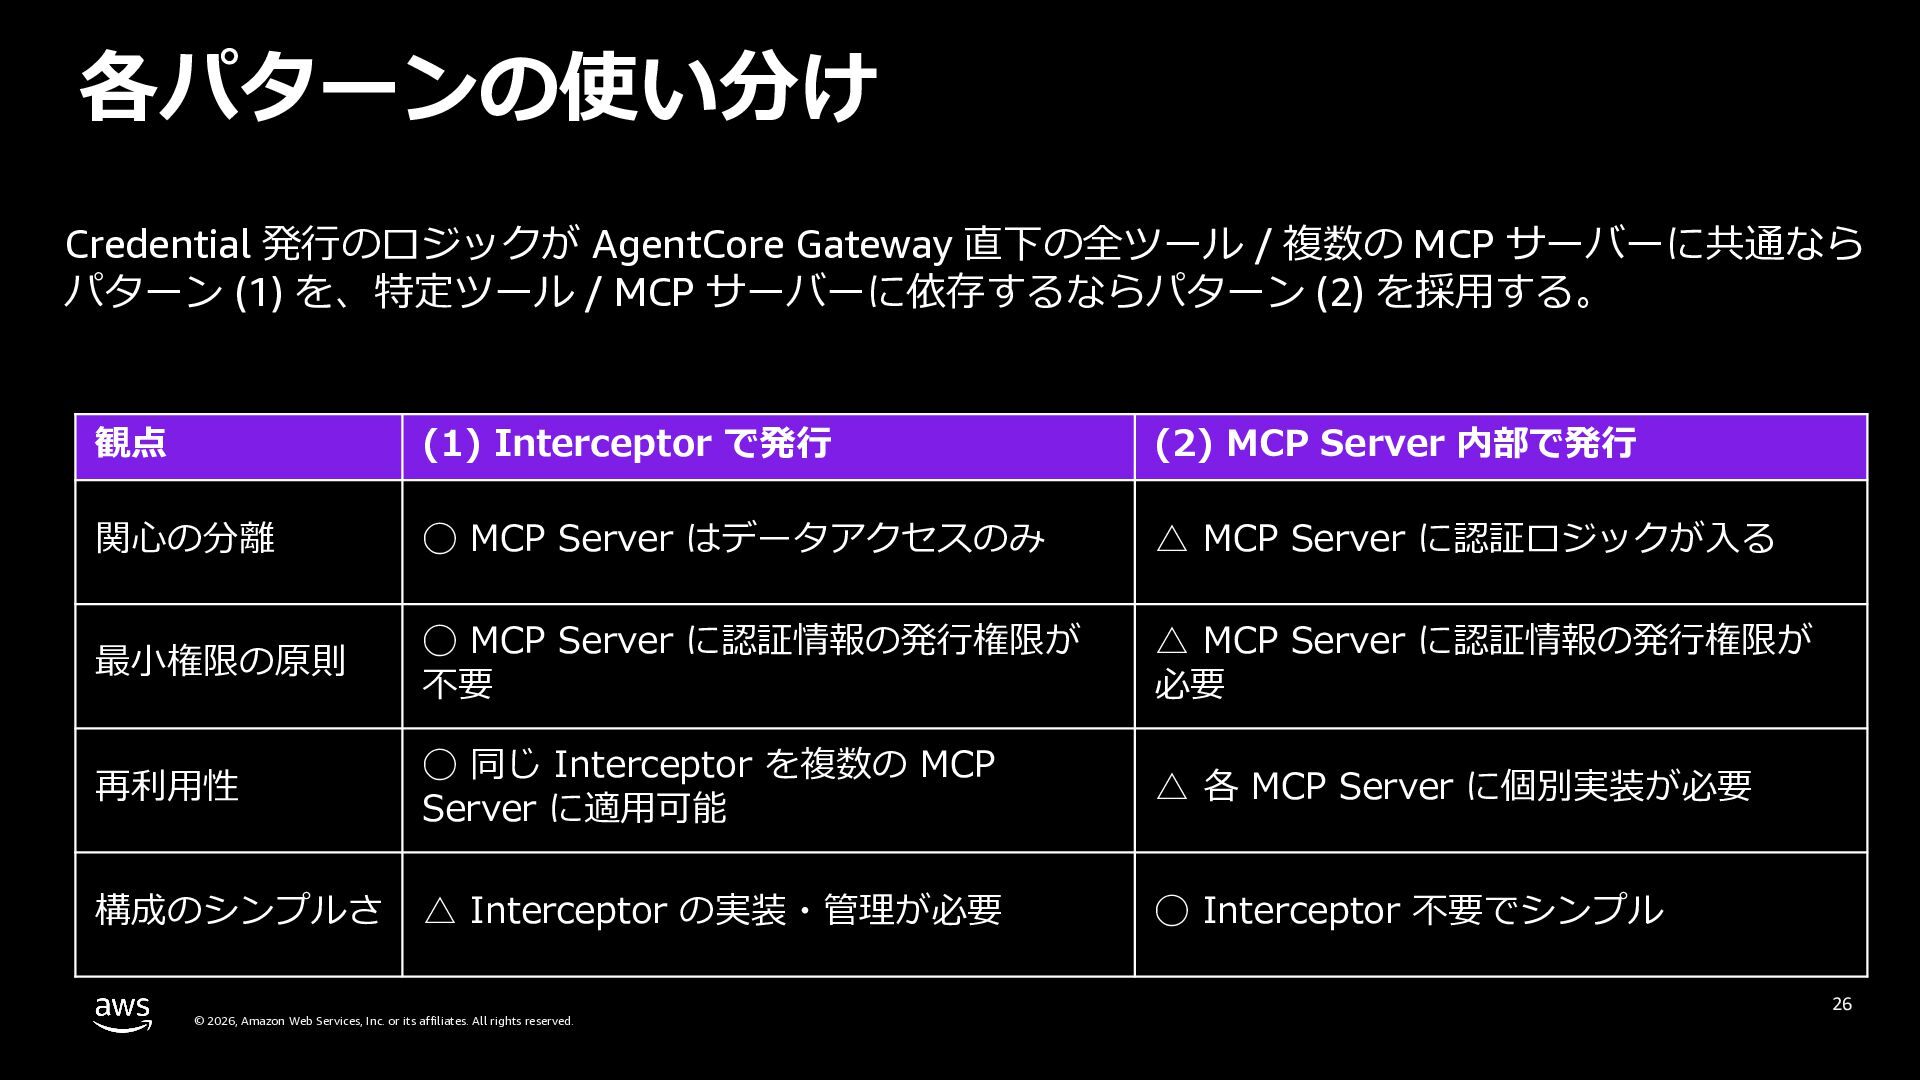
各パターンの使い分け Credential 発⾏のロジックが AgentCore Gateway 直下の全ツール / 複数の MCP サーバーに共通なら
パターン (1) を、特定ツール / MCP サーバーに依存するならパターン (2) を採⽤する。 観点 (1) Interceptor で発⾏ (2) MCP Server 内部で発⾏ 関⼼の分離 ◯ MCP Server はデータアクセスのみ △ MCP Server に認証ロジックが⼊る 最⼩権限の原則 ◯ MCP Server に認証情報の発⾏権限が 不要 △ MCP Server に認証情報の発⾏権限が 必要 再利⽤性 ◯ 同じ Interceptor を複数の MCP Server に適⽤可能 △ 各 MCP Server に個別実装が必要 構成のシンプルさ △ Interceptor の実装・管理が必要 ◯ Interceptor 不要でシンプル © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 28 -
(再掲) パターン 1: Interceptor で Credential を発⾏ ID Token を
AgentCore Gateway Interceptor にヘッダー伝播し、Interceptor 上で Credential (⼀時認証キー) に交換して、 MCP サーバーに伝播する。 ID Token を⼀時認証 キーに交換 ID Token tenant A tenant B ⼀時認証キー Gateway Interceptor (Lambda) Agent ⼀時認証キーを利⽤ してクエリ 各ユーザーの⼀時認証キーの テナント情報を評価し権限制御 ⼀時認証キー AgentCore Gateway MCP Server (AgentCore Runtime) データ基盤 本発表はこのパターン1を利⽤したユースケースで解説します。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 29 -
本発表のユースケース: AgentCore x Lake Formation による データの FGAC © 2026,
Amazon Web Services, Inc. or its affiliates. All rights reserved. 30 -
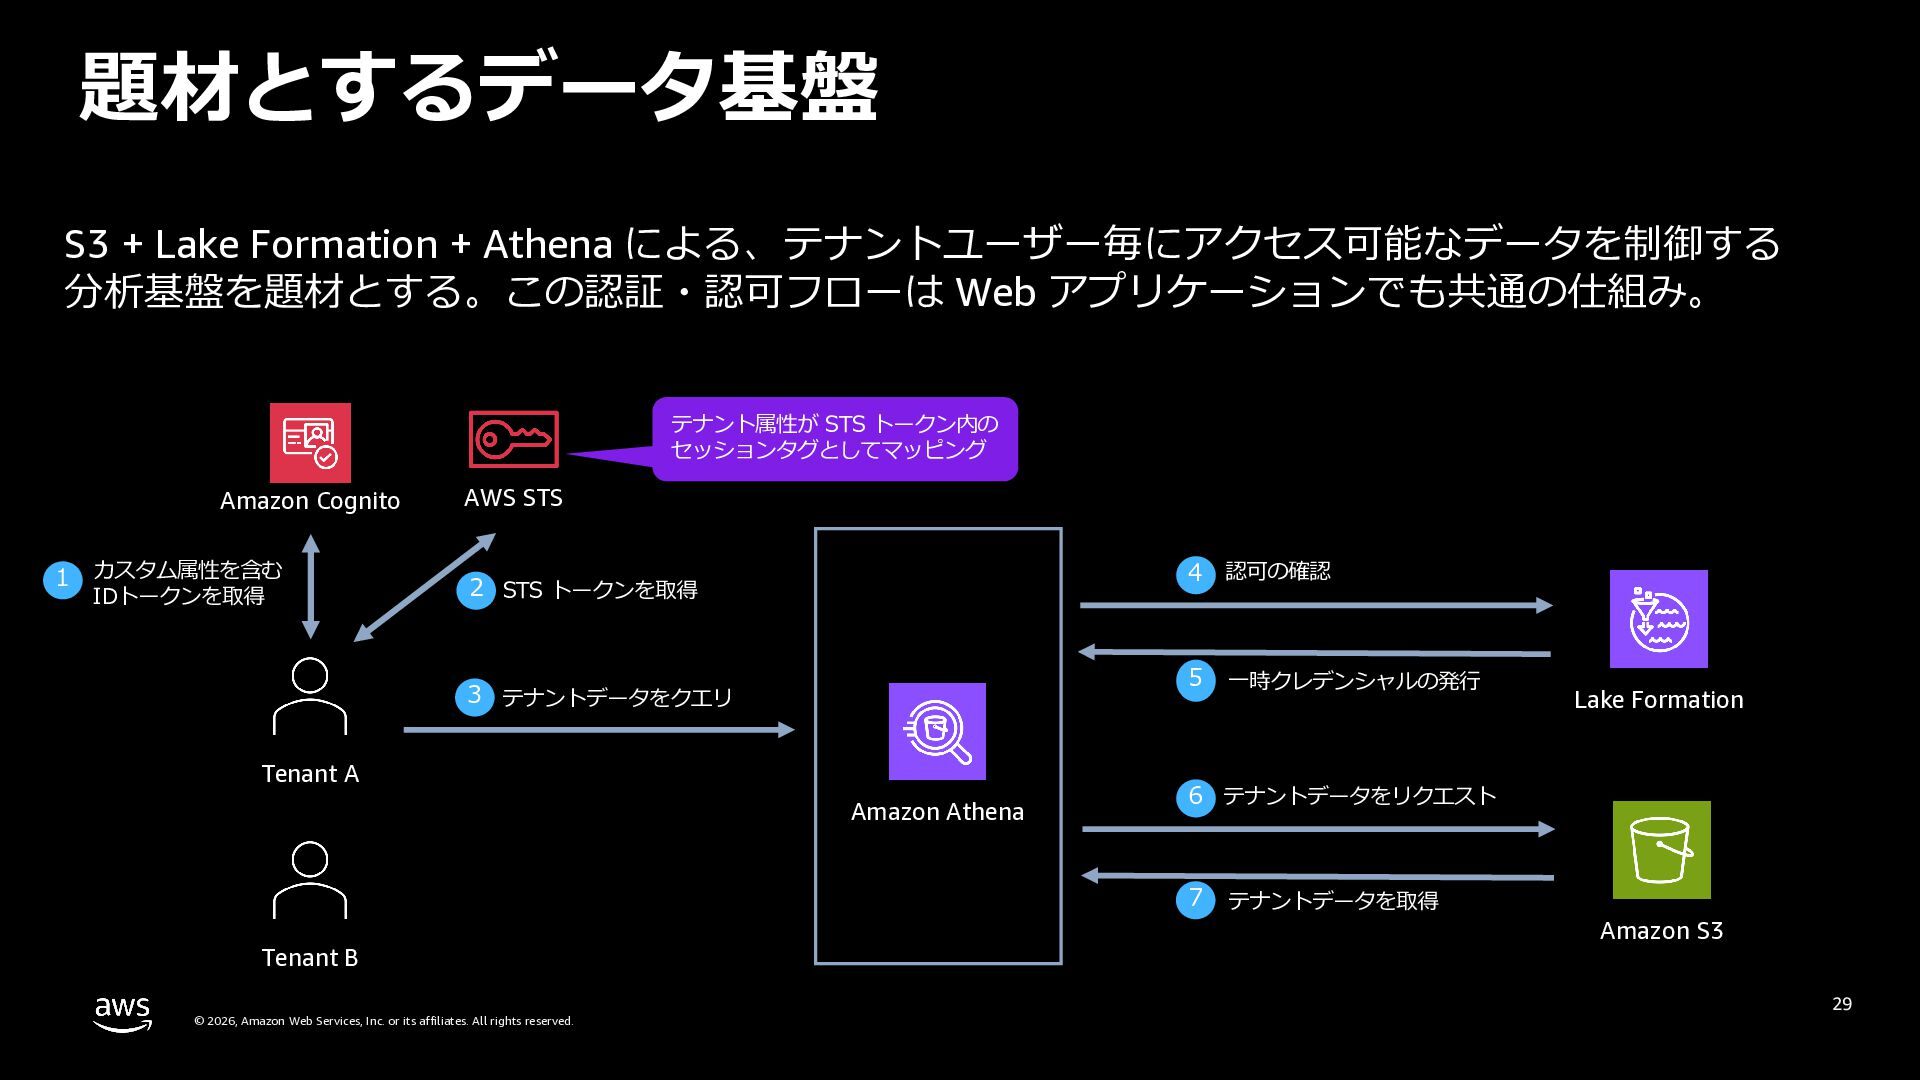
題材とするデータ基盤 S3 + Lake Formation + Athena による、テナントユーザー毎にアクセス可能なデータを制御する 分析基盤を題材とする。この認証・認可フローは Web
アプリケーションでも共通の仕組み。 テナント属性が STS トークン内の セッションタグとしてマッピング Amazon Cognito 1 カスタム属性を含む IDトークンを取得 AWS STS 4 認可の確認 2 STS トークンを取得 5 3 テナントデータをクエリ Amazon Athena © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Lake Formation 6 テナントデータをリクエスト 7 Tenant B ⼀時クレデンシャルの発⾏ テナントデータを取得 Amazon S3 31 -
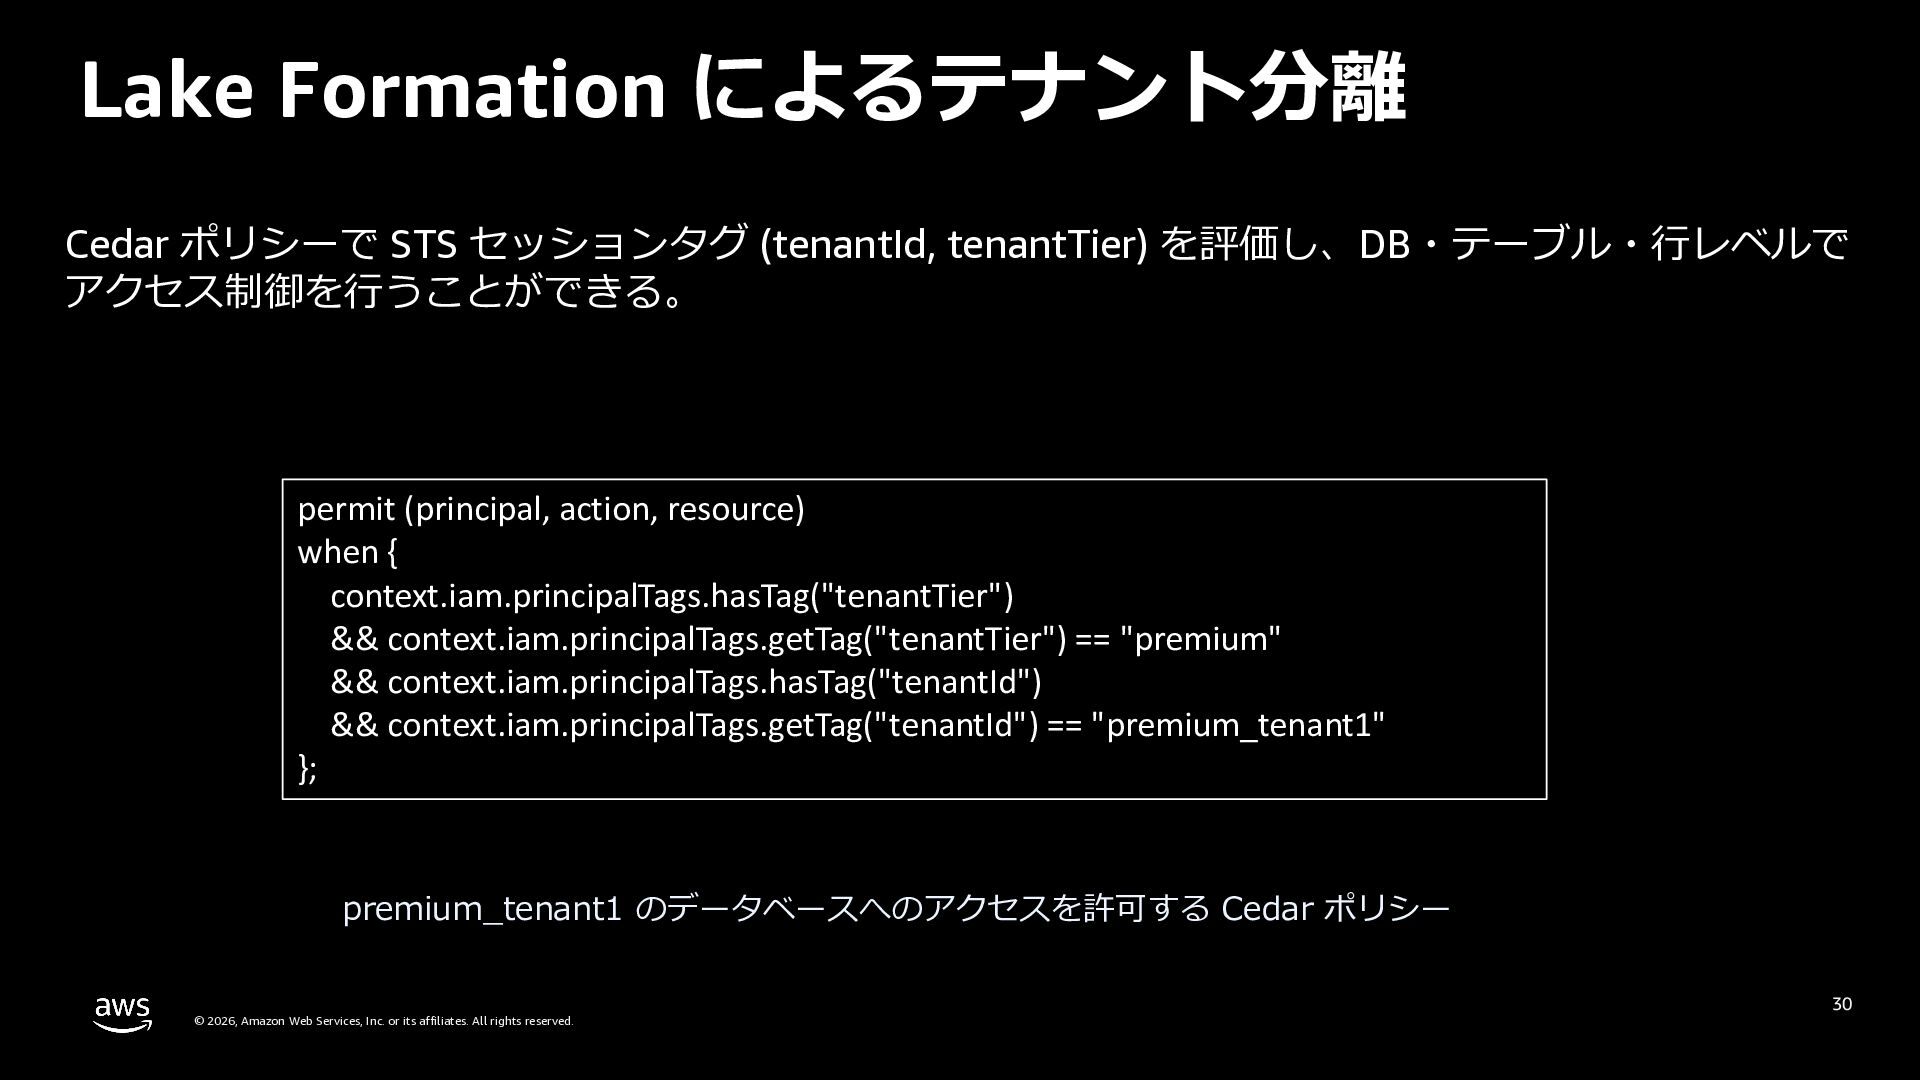
Lake Formation によるテナント分離 Cedar ポリシーで STS セッションタグ (tenantId, tenantTier) を評価し、DB・テーブル・⾏レベルで
アクセス制御を⾏うことができる。 permit (principal, action, resource) when { context.iam.principalTags.hasTag("tenantTier") && context.iam.principalTags.getTag("tenantTier") == "premium" && context.iam.principalTags.hasTag("tenantId") && context.iam.principalTags.getTag("tenantId") == "premium_tenant1" }; premium_tenant1 のデータベースへのアクセスを許可する Cedar ポリシー © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 32 -
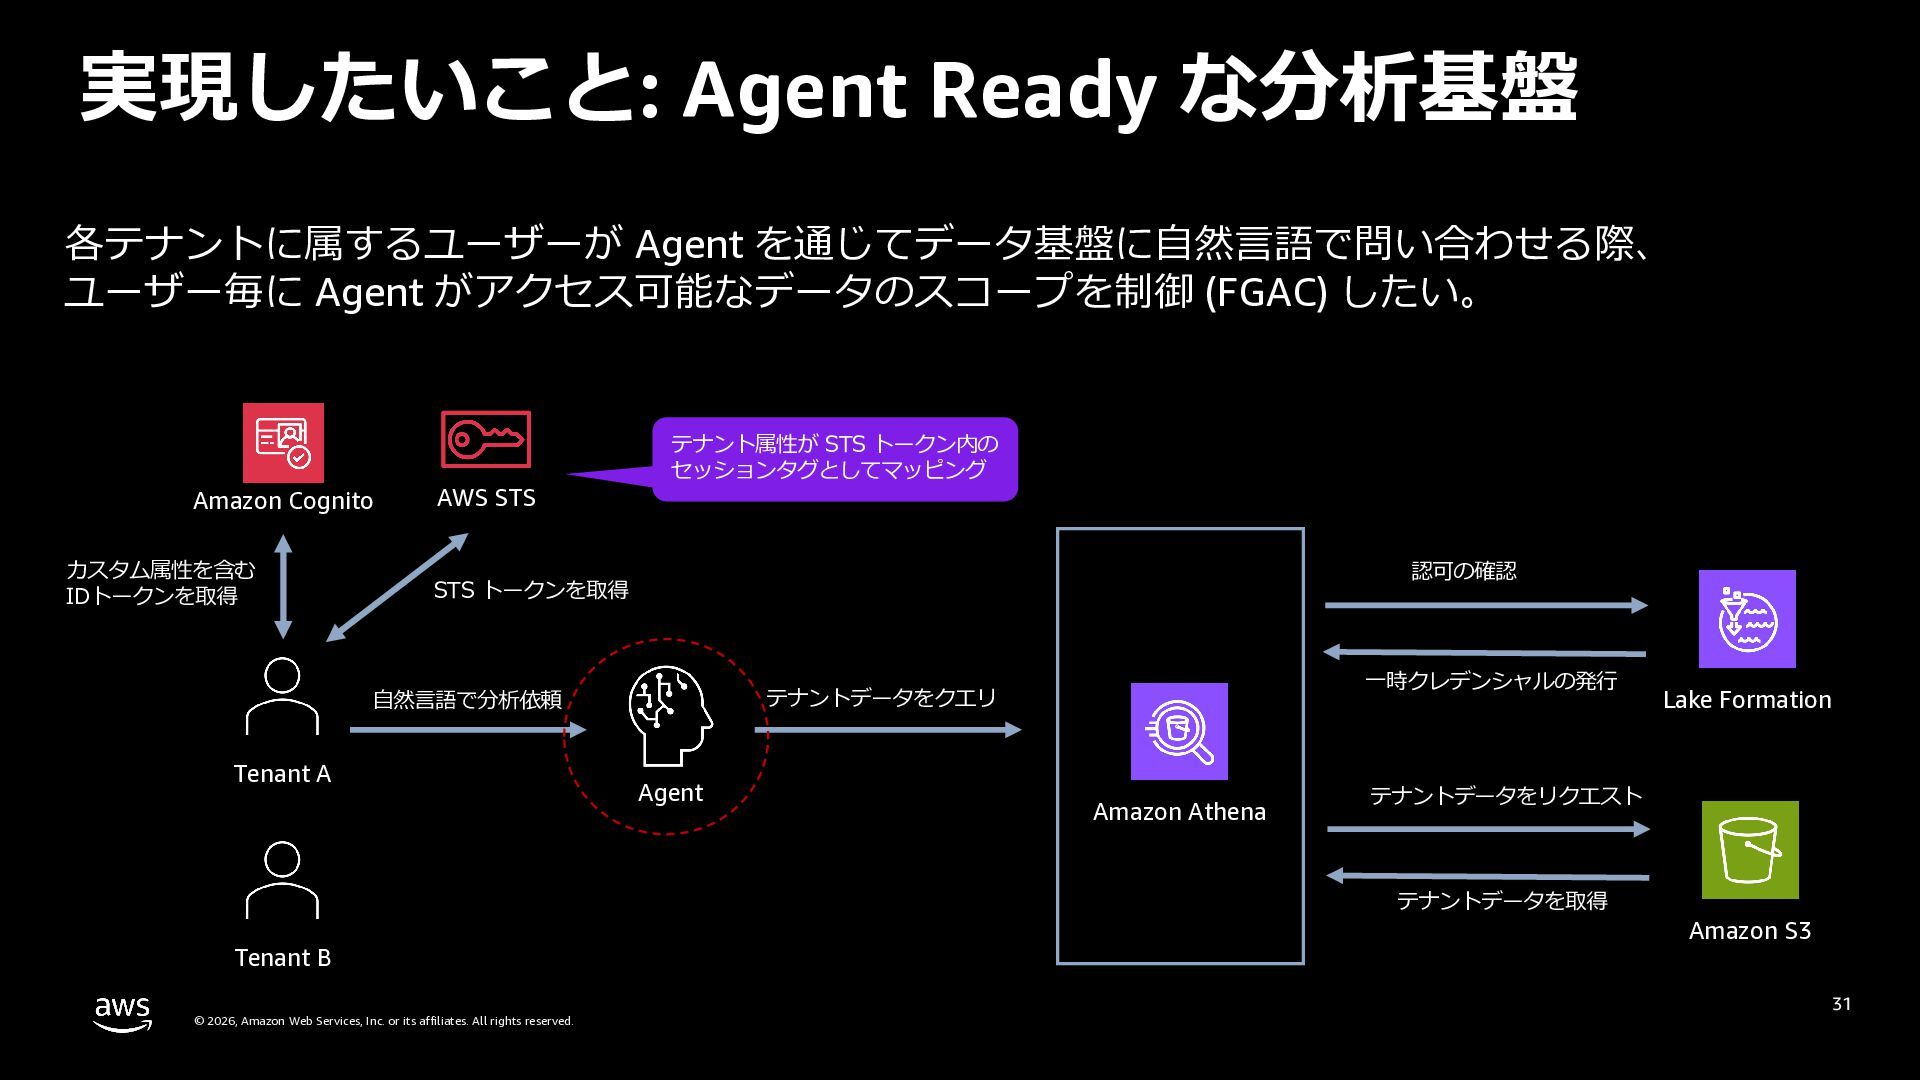
実現したいこと: Agent Ready な分析基盤 各テナントに属するユーザーが Agent を通じてデータ基盤に⾃然⾔語で問い合わせる際、 ユーザー毎に Agent がアクセス可能なデータのスコープを制御
(FGAC) したい。 Amazon Cognito カスタム属性を含む IDトークンを取得 AWS STS テナント属性が STS トークン内の セッションタグとしてマッピング 認可の確認 STS トークンを取得 Tenant A ⼀時クレデンシャルの発⾏ テナントデータをクエリ ⾃然⾔語で分析依頼 Agent Amazon Athena テナントデータをリクエスト テナントデータを取得 Tenant B © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Lake Formation Amazon S3 33 -
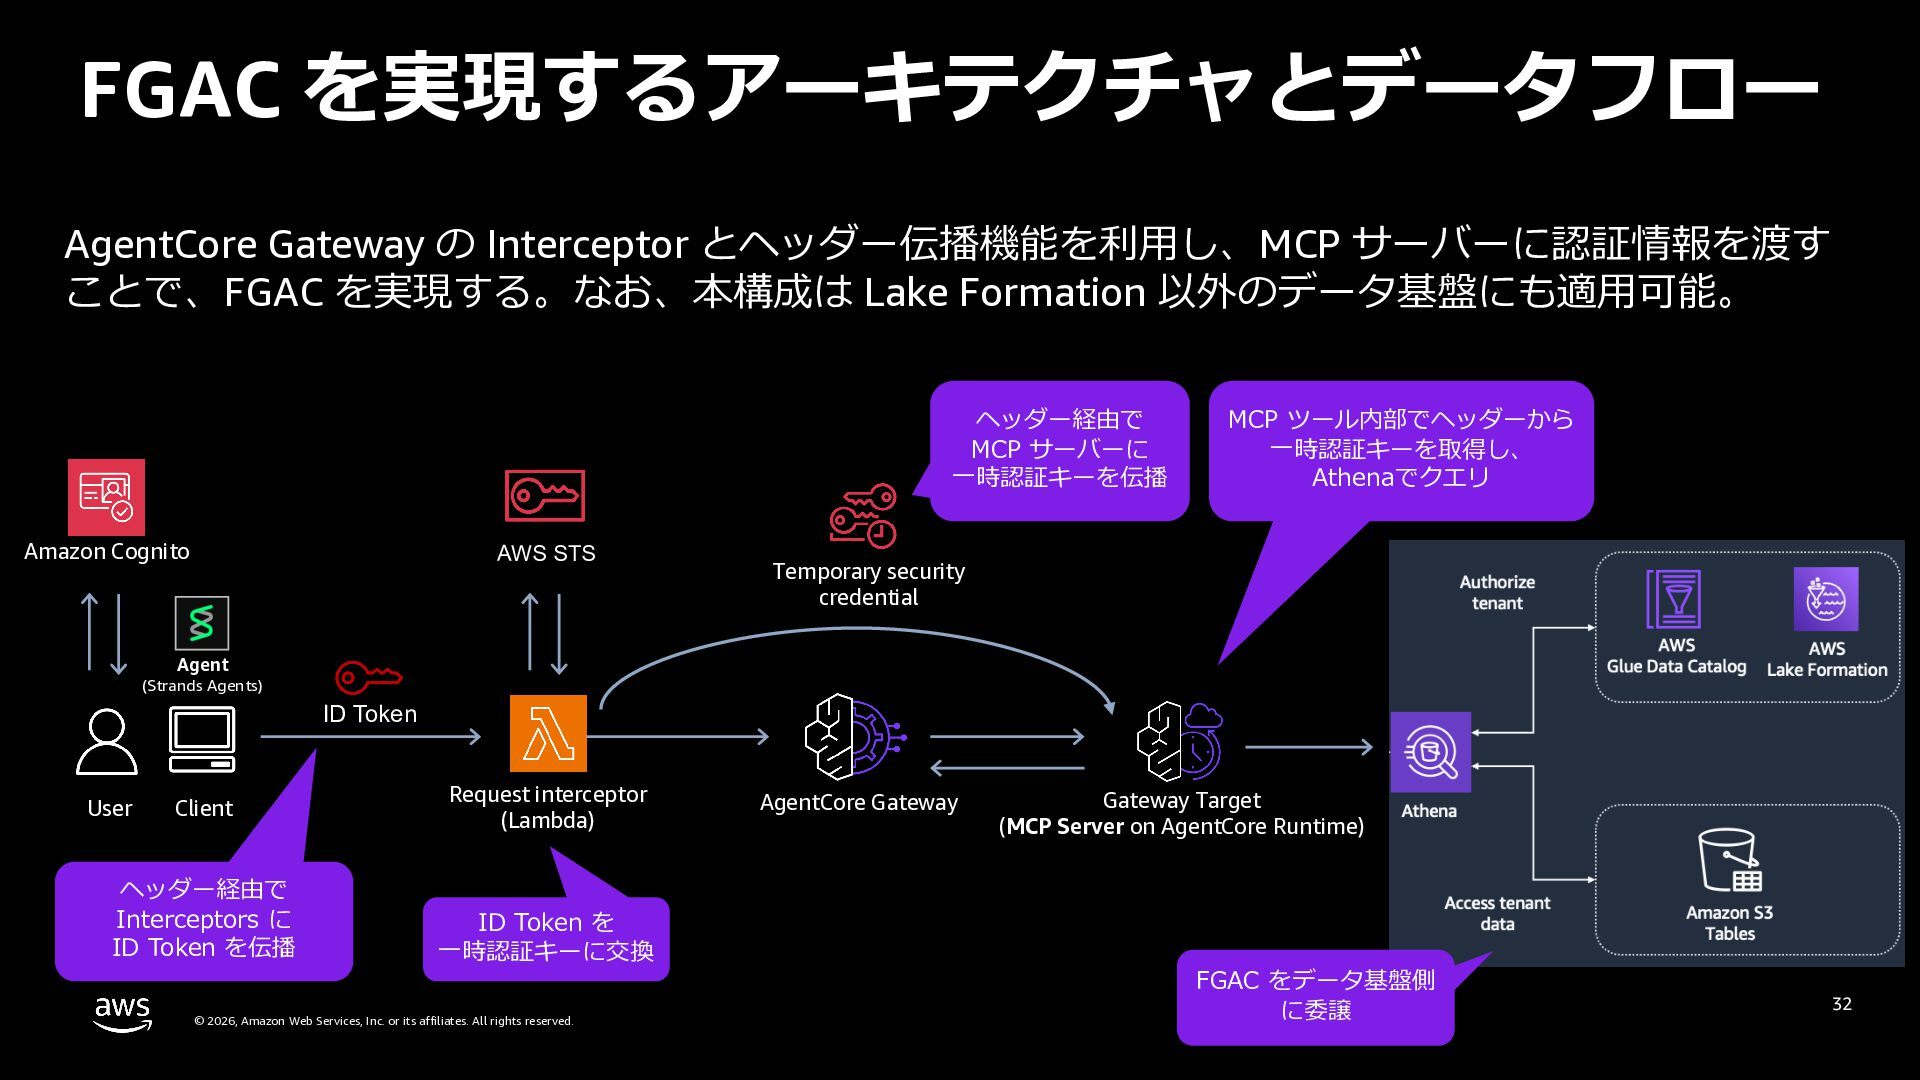
FGAC を実現するアーキテクチャとデータフロー AgentCore Gateway の Interceptor とヘッダー伝播機能を利⽤し、MCP サーバーに認証情報を渡す ことで、FGAC を実現する。なお、本構成は
Lake Formation 以外のデータ基盤にも適⽤可能。 ヘッダー経由で MCP サーバーに ⼀時認証キーを伝播 Amazon Cognito AWS STS MCP ツール内部でヘッダーから ⼀時認証キーを取得し、 Athenaでクエリ Temporary security credential Agent (Strands Agents) ID Token User Client ヘッダー経由で Interceptors に ID Token を伝播 Request interceptor (Lambda) ID Token を ⼀時認証キーに交換 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. AgentCore Gateway Gateway Target (MCP Server on AgentCore Runtime) FGAC をデータ基盤側 に委譲 34 -
AgentCore Gateway カスタムヘッダー 伝播の Dive Deep © 2026, Amazon Web
Services, Inc. or its affiliates. All rights reserved. 35 -
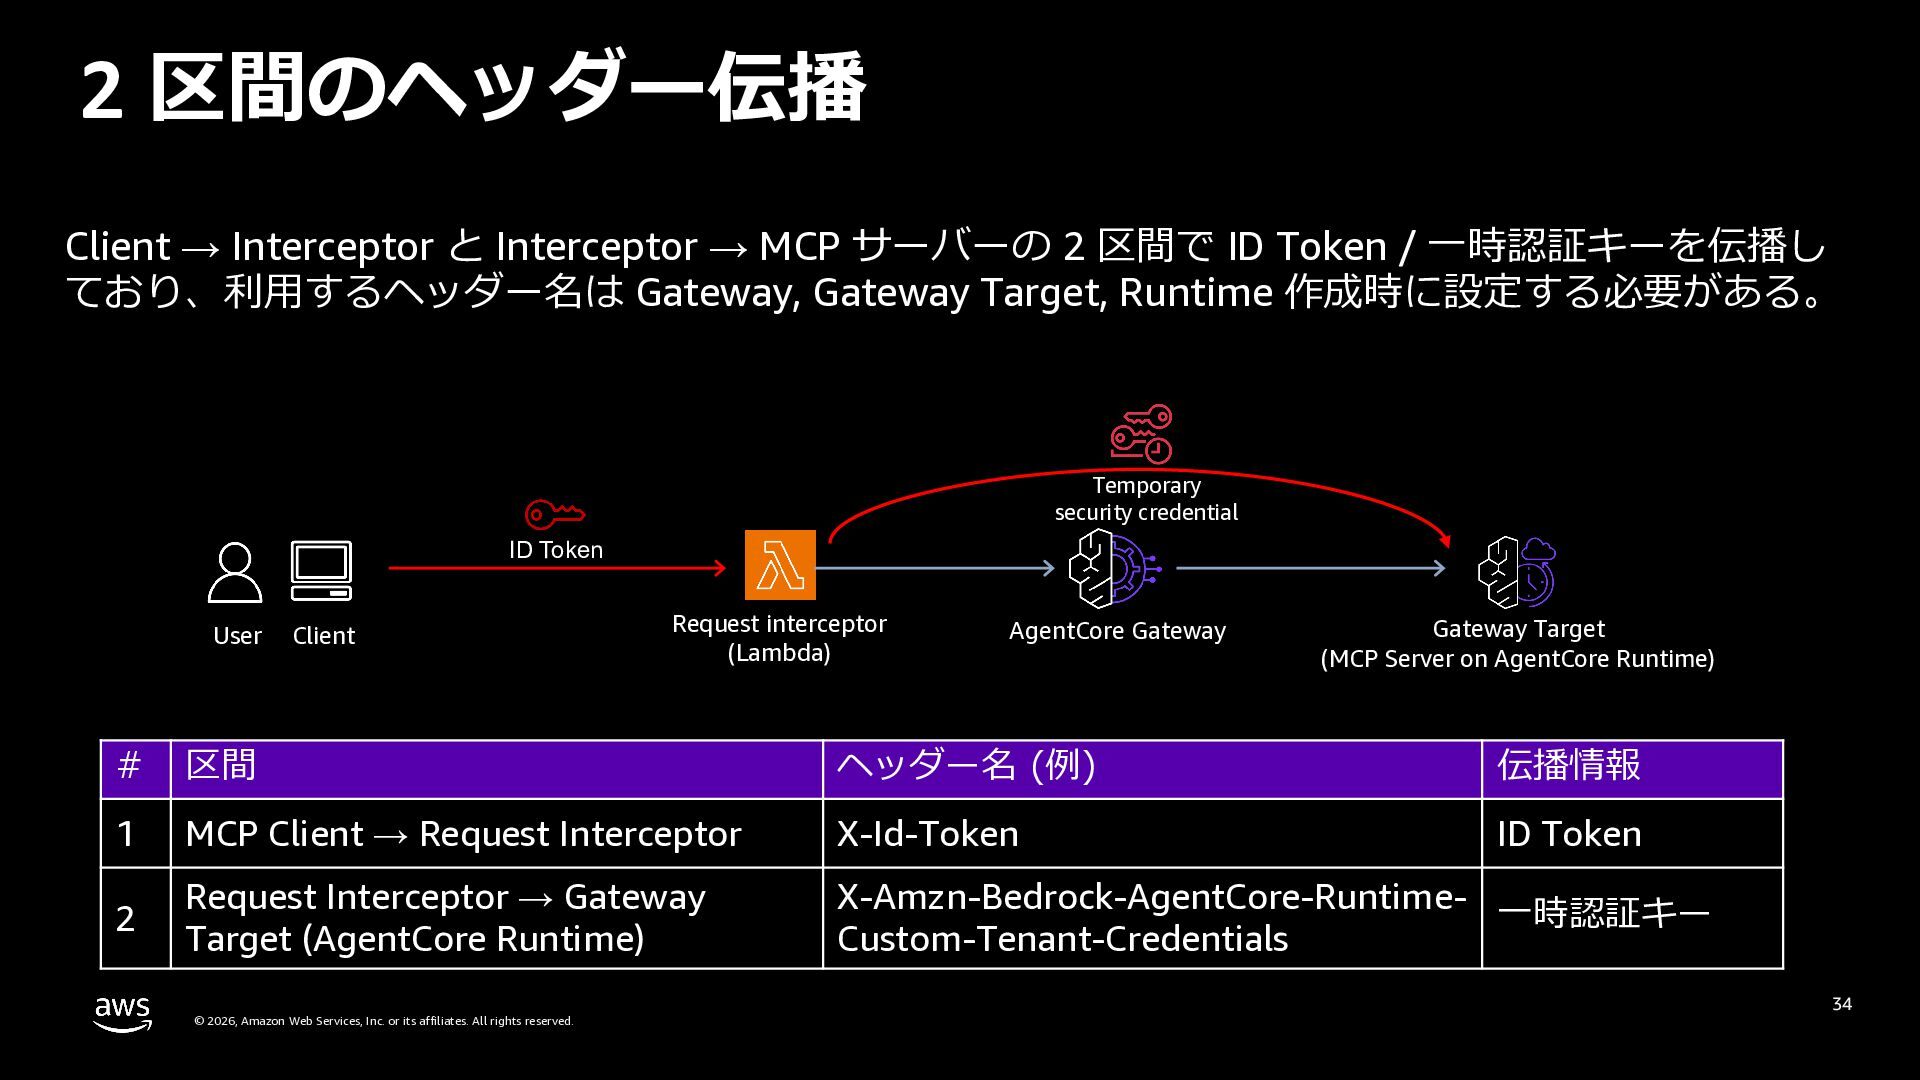
2 区間のヘッダー伝播 Client → Interceptor と Interceptor → MCP サーバーの
2 区間で ID Token / ⼀時認証キーを伝播し ており、利⽤するヘッダー名は Gateway, Gateway Target, Runtime 作成時に設定。 Temporary security credential ID Token User Client Request interceptor (Lambda) AgentCore Gateway Gateway Target (MCP Server on AgentCore Runtime) # 区間 ヘッダー名 (例) 伝播情報 1 MCP Client → Request Interceptor X-Id-Token ID Token 2 Request Interceptor → Gateway Target (AgentCore Runtime) X-Amzn-Bedrock-AgentCore-Runtime- ⼀時認証キー Custom-Tenant-Credentials © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 36 -
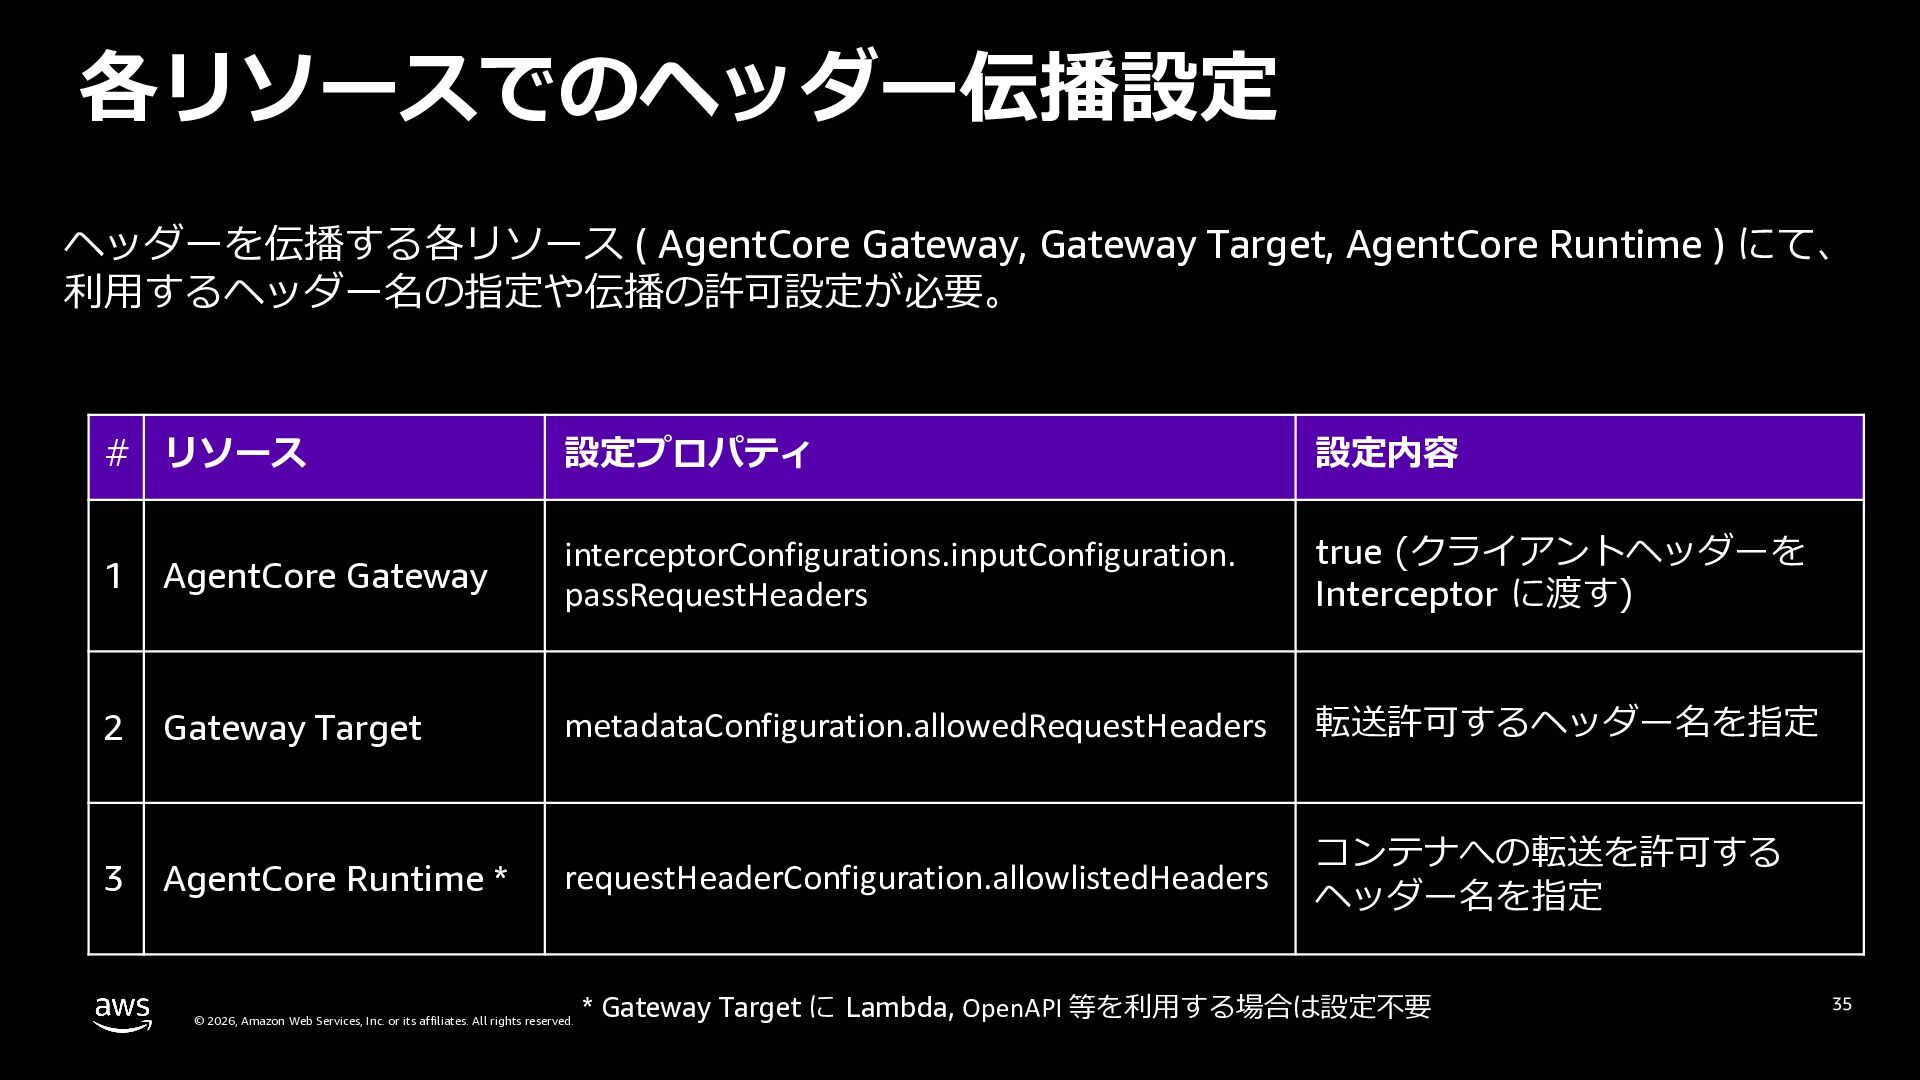
各リソースでのヘッダー伝播設定 ヘッダーを伝播する各リソース ( AgentCore Gateway, Gateway Target, AgentCore Runtime )
にて、 利⽤するヘッダー名の指定や伝播の許可設定が必要。 # リソース 設定プロパティ 設定内容 1 AgentCore Gateway interceptorConfigurations.inputConfiguration. passRequestHeaders true (クライアントヘッダーを Interceptor に渡す) 2 Gateway Target metadataConfiguration.allowedRequestHeaders 転送許可するヘッダー名を指定 3 AgentCore Runtime * requestHeaderConfiguration.allowlistedHeaders コンテナへの転送を許可する ヘッダー名を指定 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. * Gateway Target に Lambda 等を利⽤する場合は設定不要 37 -
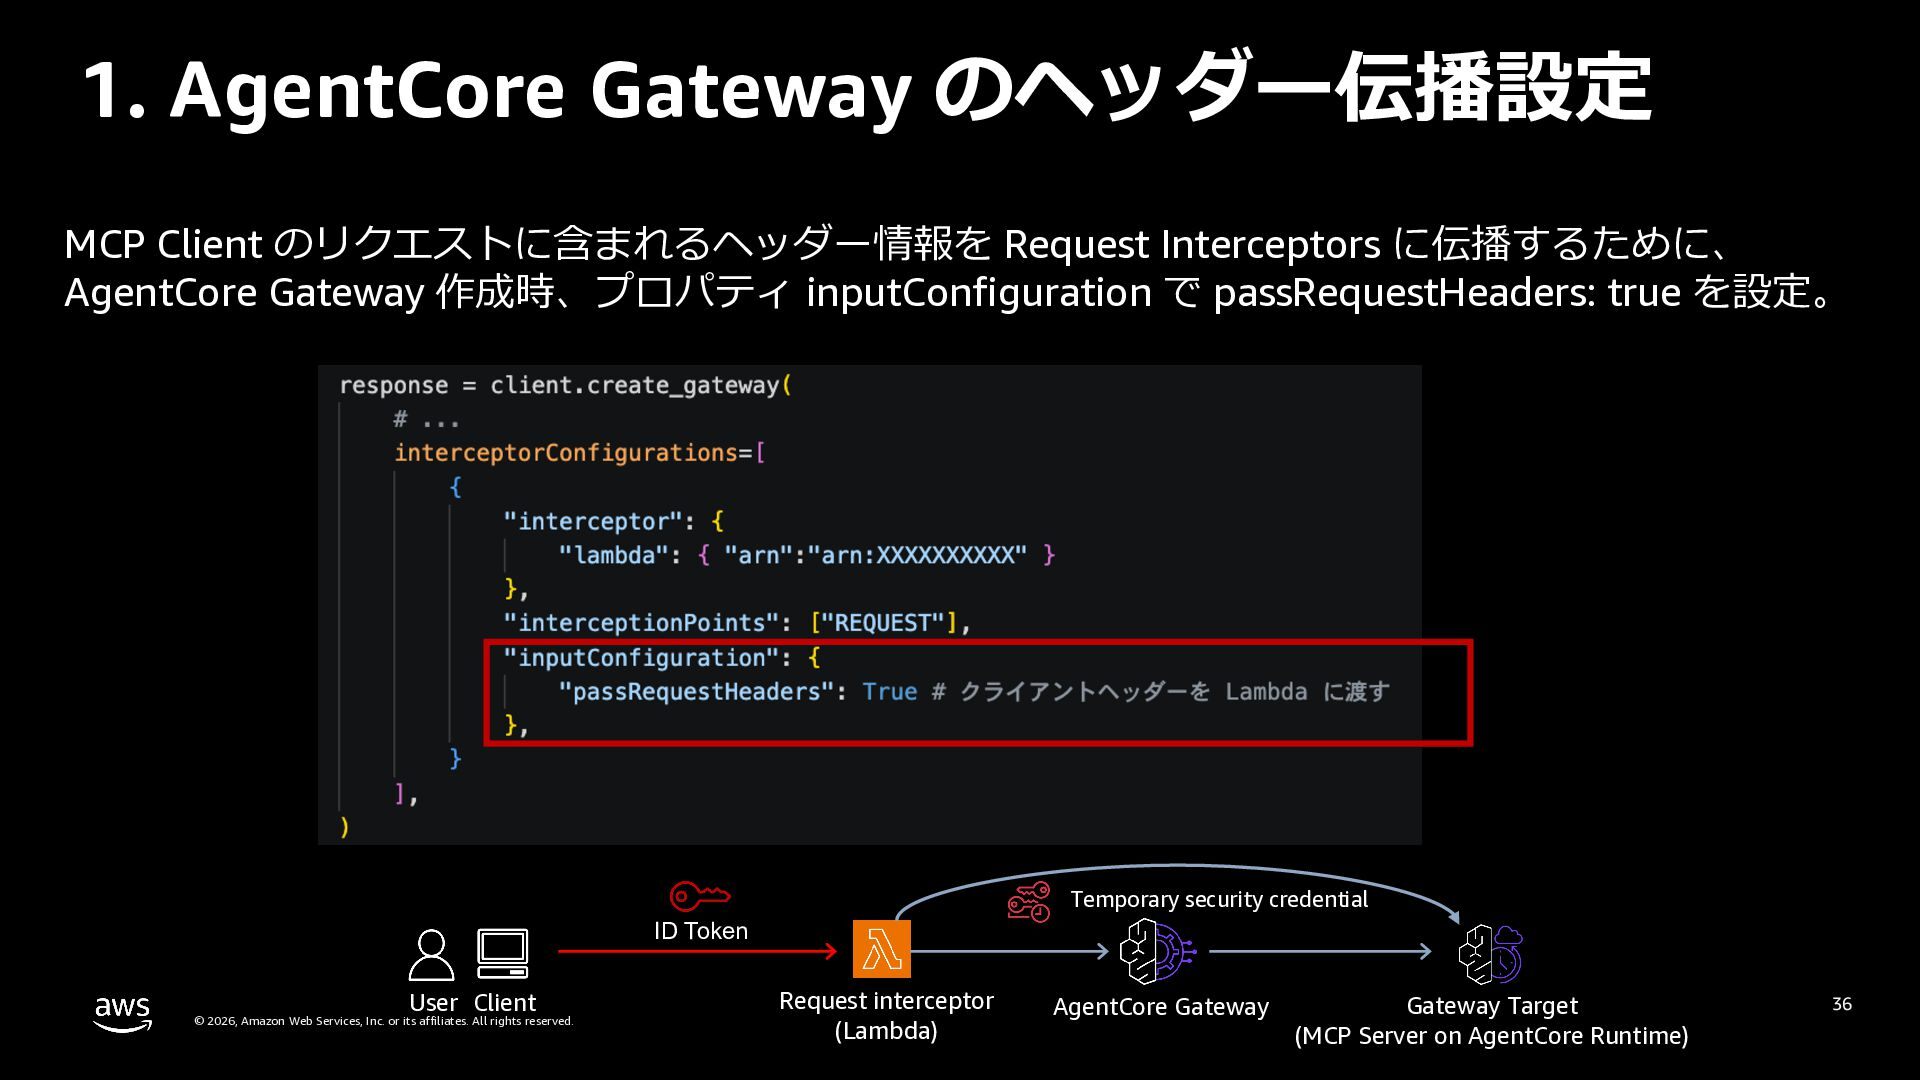
1. AgentCore Gateway のヘッダー伝播設定 MCP Client のリクエストに含まれるヘッダー情報を Request Interceptors に伝播するために、
AgentCore Gateway 作成時、プロパティ inputConfiguration で passRequestHeaders: true を設定。 Temporary security credential ID Token User Client © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Request interceptor (Lambda) AgentCore Gateway Gateway Target (MCP Server on AgentCore Runtime) 38 -
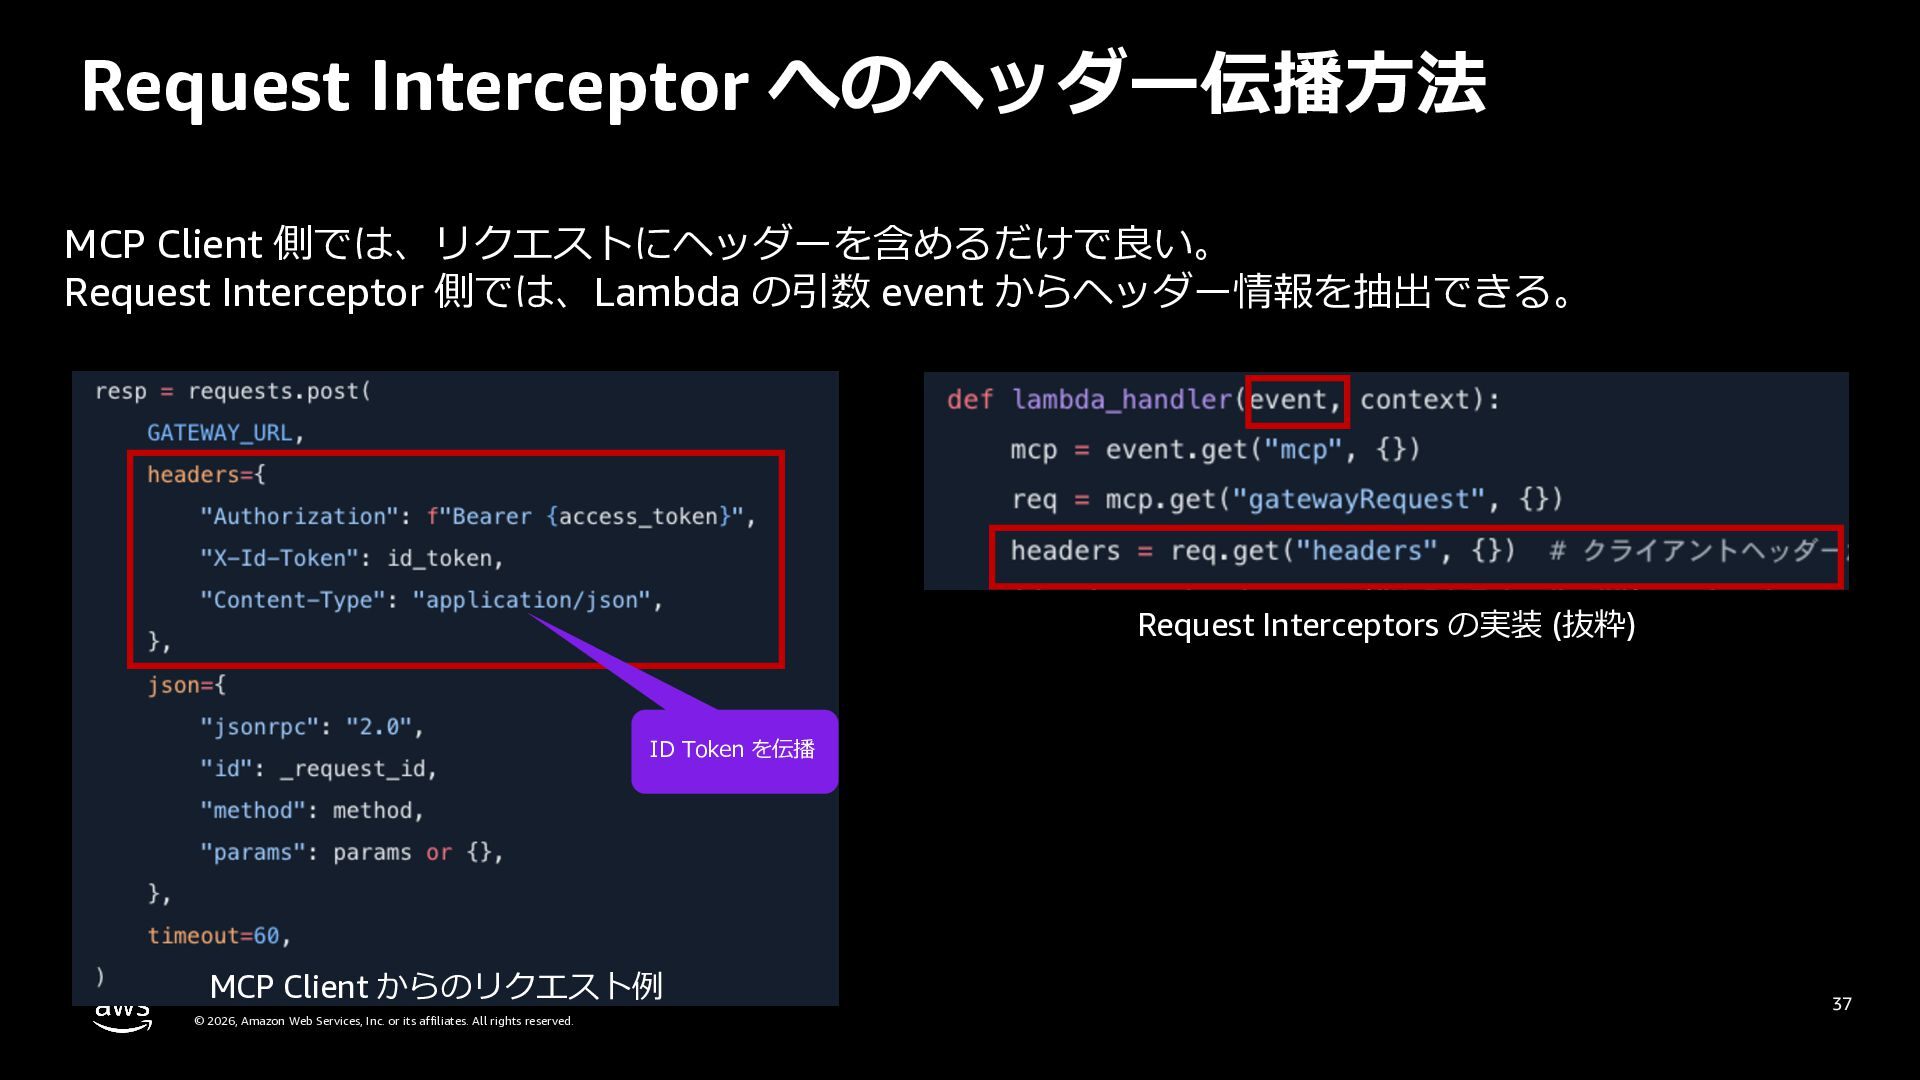
Request Interceptor へのヘッダー伝播⽅法 MCP Client 側では、リクエストにヘッダーを含めるだけで良い。 Request Interceptor 側では、Lambda の引数
event からヘッダー情報を抽出できる。 Request Interceptors の実装 (抜粋) ID Token を伝播 MCP Client からのリクエスト例 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 39 -
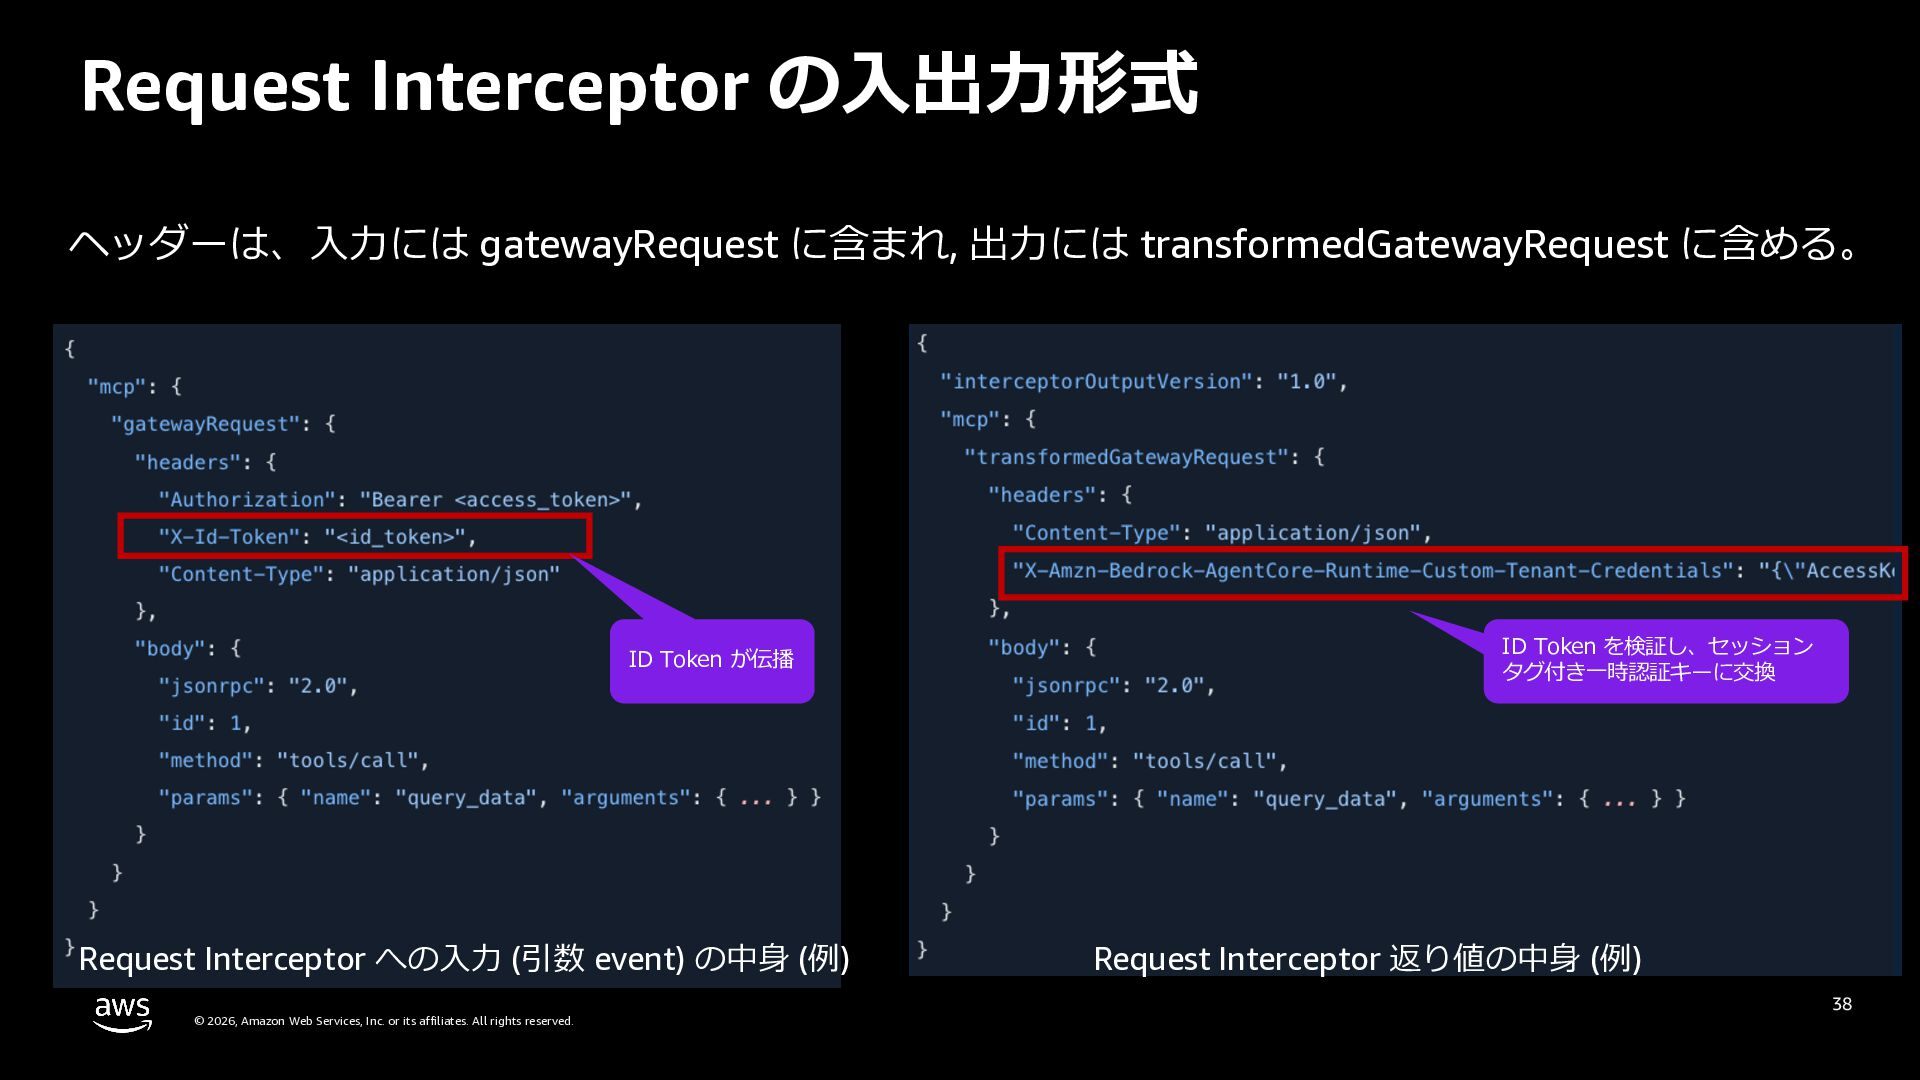
Request Interceptor の⼊出⼒形式 ヘッダーは、⼊⼒には gatewayRequest に含まれ, 出⼒には transformedGatewayRequest に含める。 ID
Token が伝播 Request Interceptor への⼊⼒ (引数 event) の中⾝ (例) © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. ID Token を検証し、セッション タグ付き⼀時認証キーに交換 Request Interceptor 返り値の中⾝ (例) 40 -
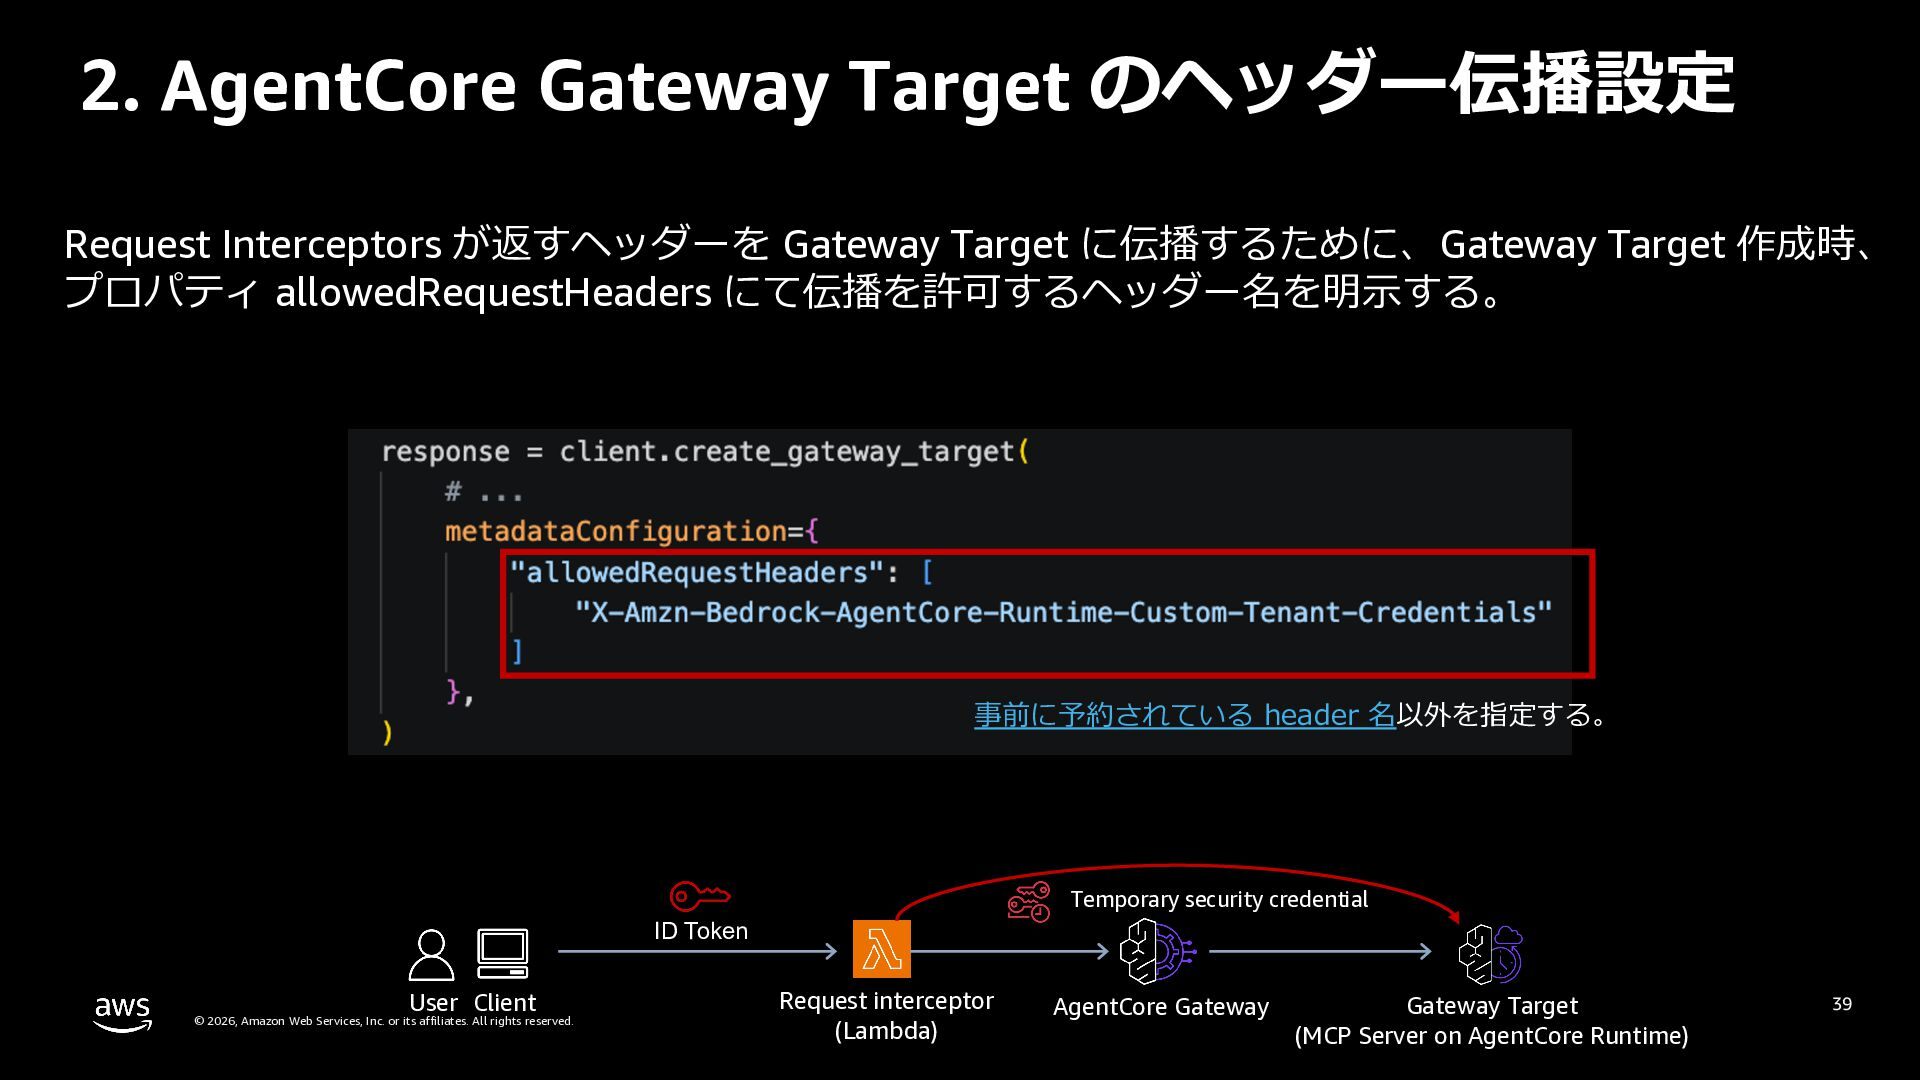
2. AgentCore Gateway Target のヘッダー伝播設定 Request Interceptors が返すヘッダーを Gateway Target
に伝播するために、Gateway Target 作成時、 プロパティ allowedRequestHeaders にて伝播を許可するヘッダー名を明⽰する。 事前に予約されている header 名や、x-amzn- から始まるヘッダー名以外 を指定。(X-Amzn-Bedrock-AgentCore-Runtime-Custom-* は OK) Temporary security credential ID Token User Client © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Request interceptor (Lambda) AgentCore Gateway Gateway Target (MCP Server on AgentCore Runtime) 41 -
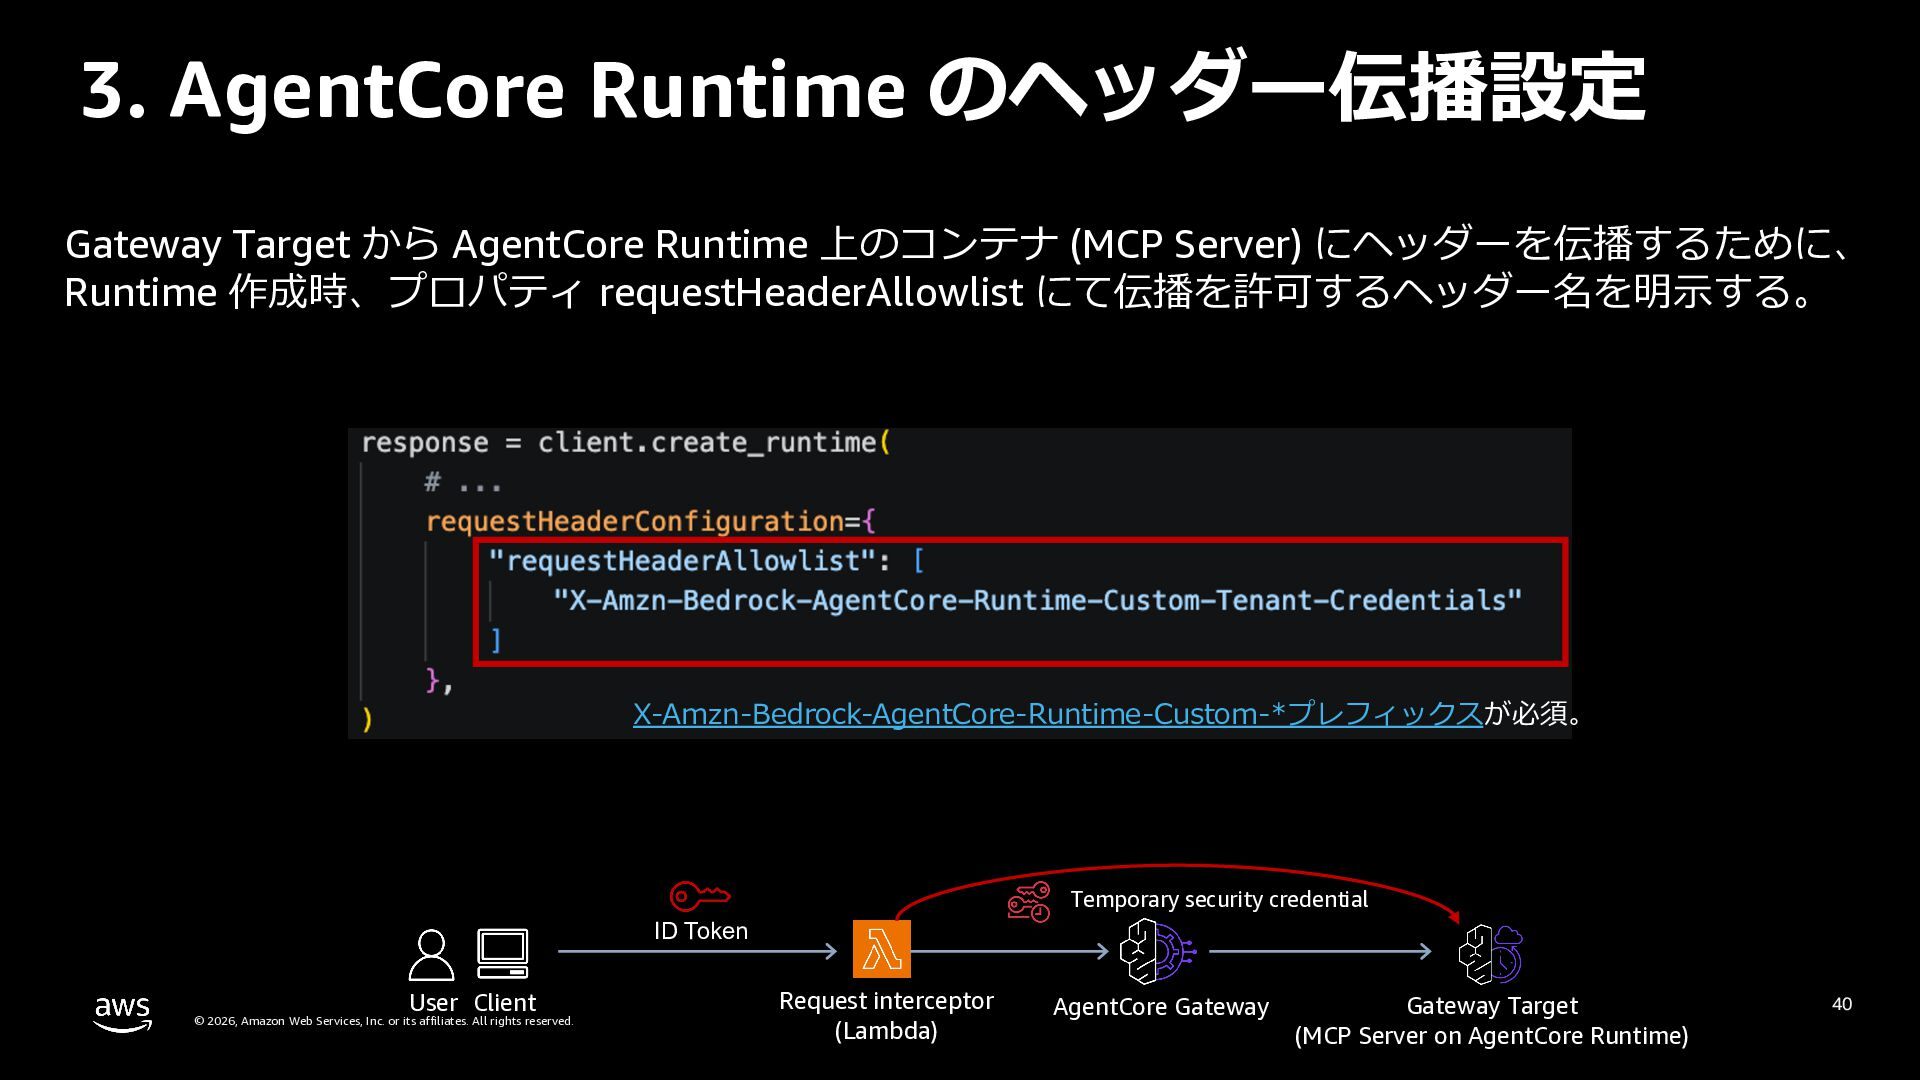
3. AgentCore Runtime のヘッダー伝播設定 Gateway Target から AgentCore Runtime 上のコンテナ
(MCP Server) にヘッダーを伝播するために、 Runtime 作成時、プロパティ requestHeaderAllowlist にて伝播を許可するヘッダー名を明⽰する。 事前に予約されている header 名や、x-amz-, x-amzn- から始まるヘッダー名以外 を指定。(X-Amzn-Bedrock-AgentCore-Runtime-Custom-* は OK) Temporary security credential ID Token User Client © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Request interceptor (Lambda) AgentCore Gateway Gateway Target (MCP Server on AgentCore Runtime) 42 -
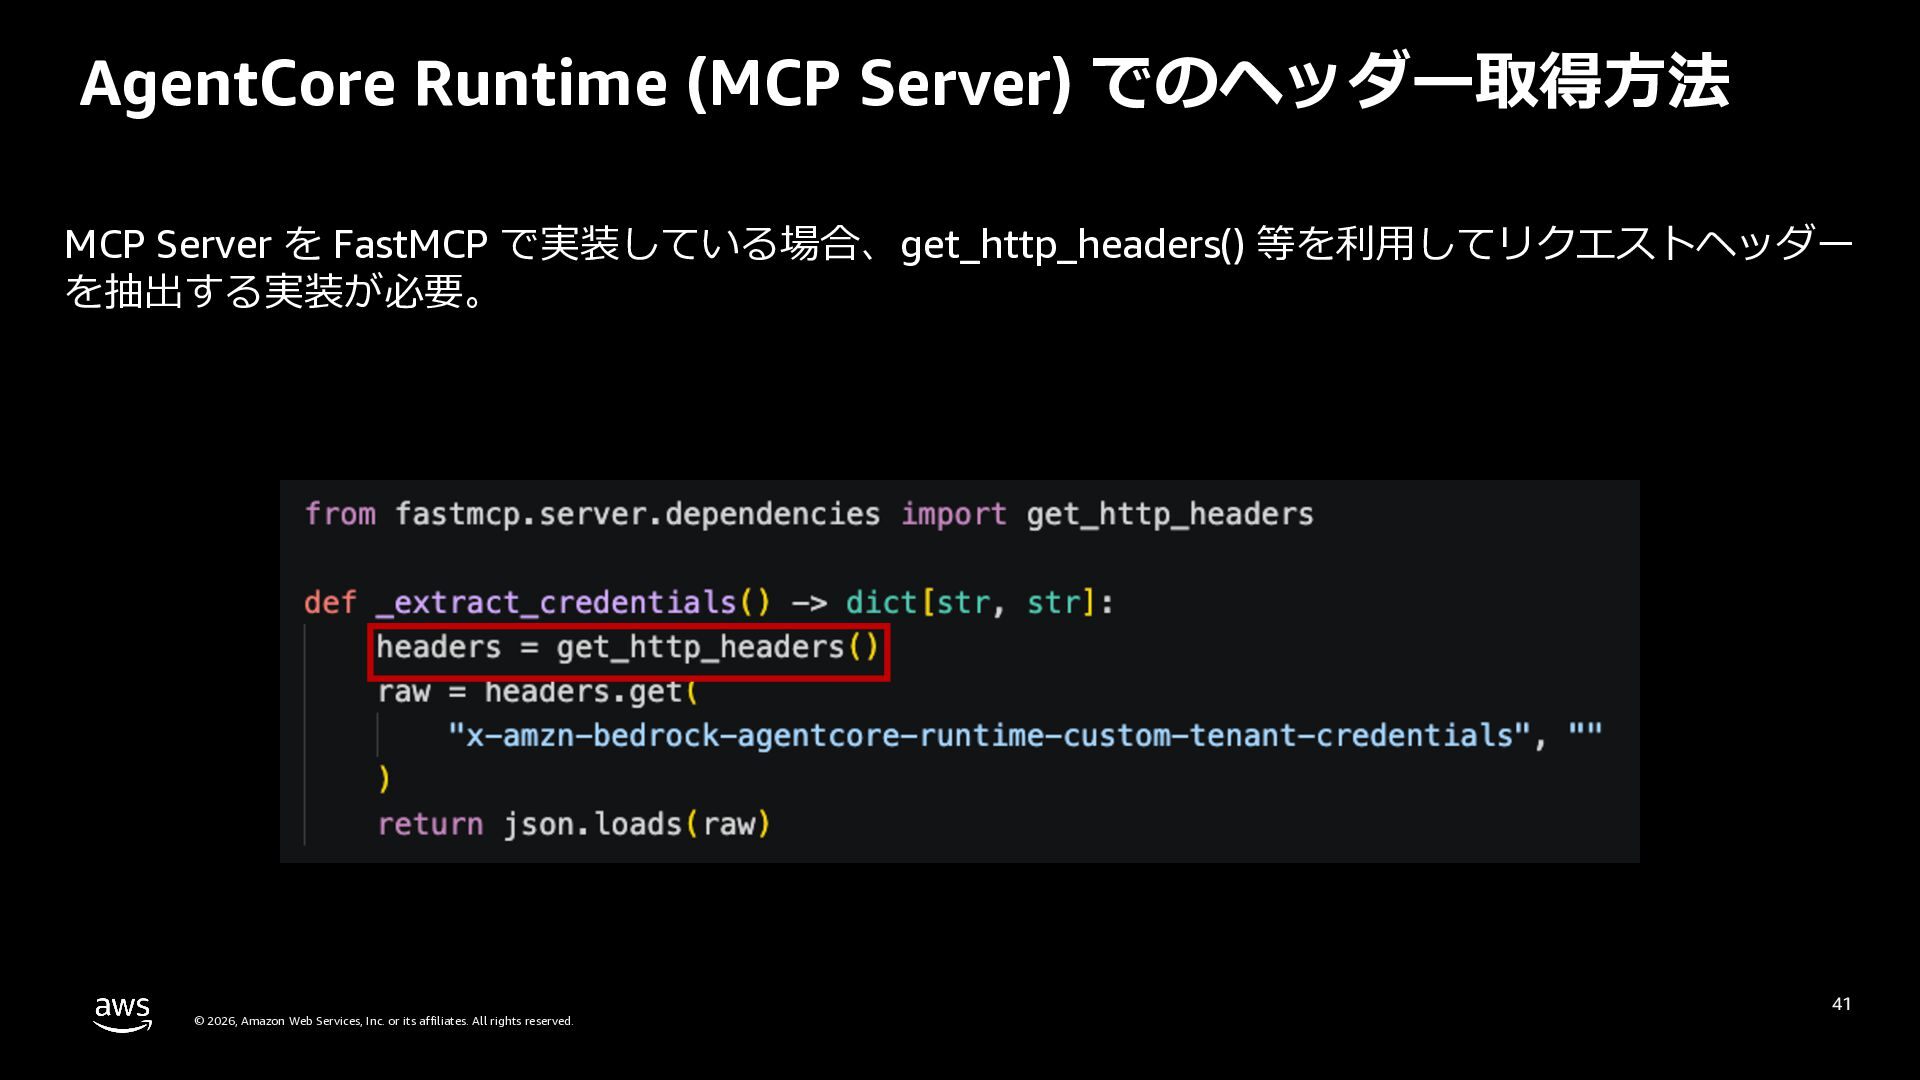
AgentCore Runtime (MCP Server) でのヘッダー取得⽅法 MCP Server を FastMCP で実装している場合、get_http_headers()
等を利⽤してリクエストヘッダー を抽出する実装が必要。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 43 -
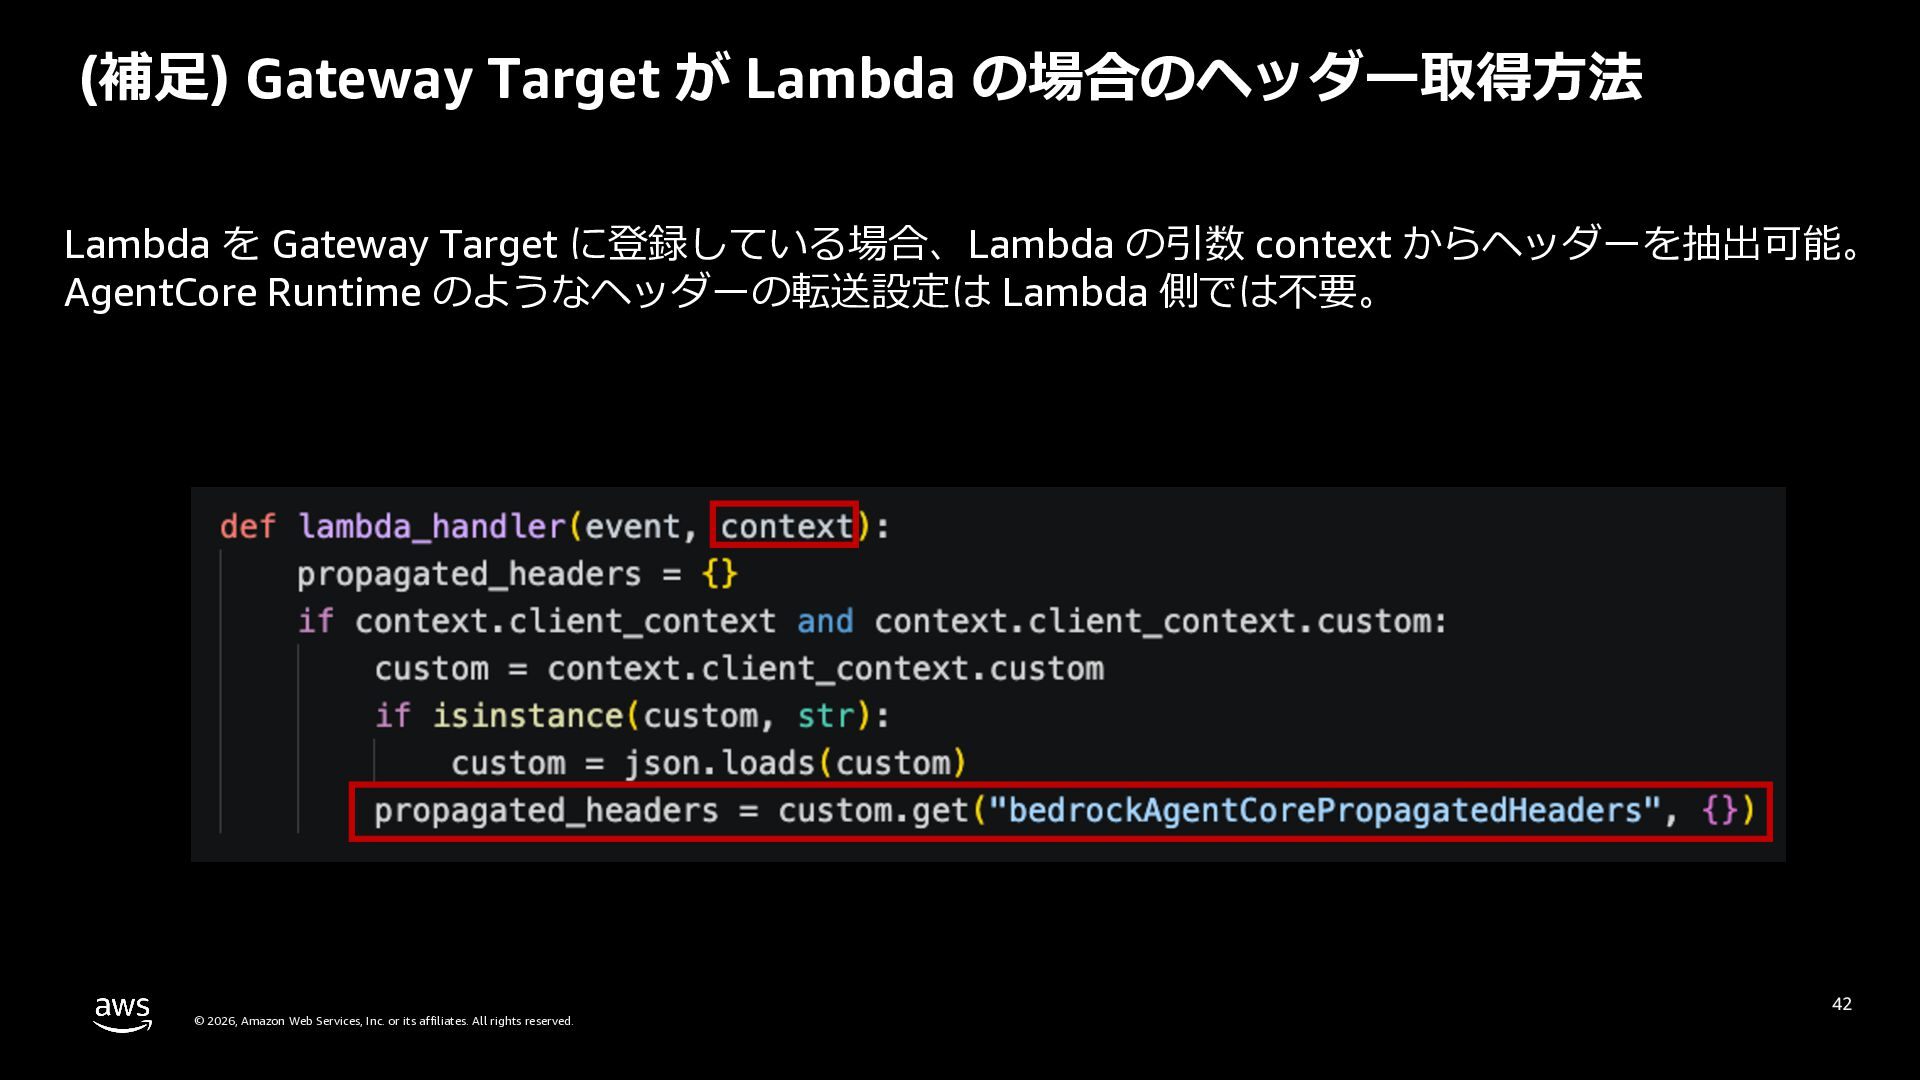
(補⾜) Gateway Target が Lambda の場合のヘッダー取得⽅法 Lambda を Gateway Target
に登録している場合、Lambda の引数 context からヘッダーを抽出可能。 AgentCore Runtime のようなヘッダーの転送設定は Lambda 側では不要。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 44 -
おわりに © 2026, Amazon Web Services, Inc. or its affiliates.
All rights reserved. 45 -
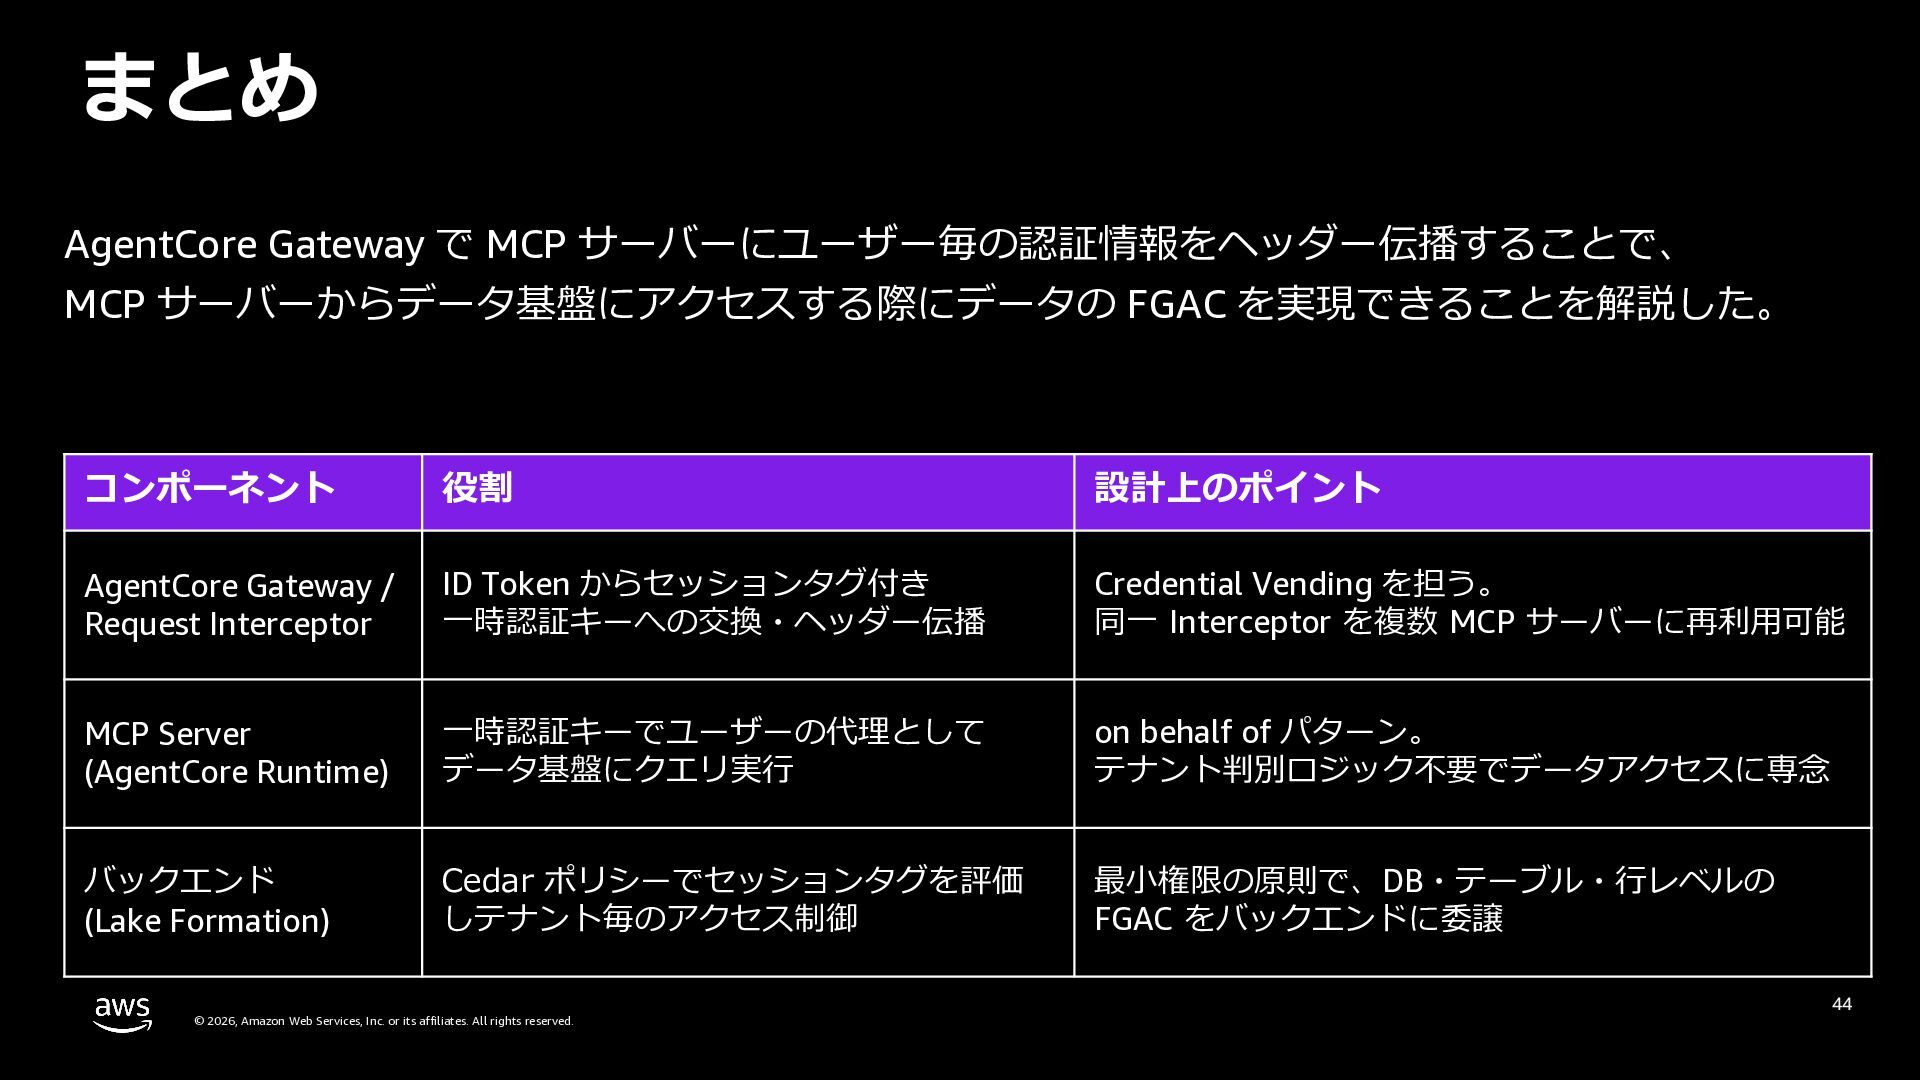
まとめ AgentCore Gateway で MCP サーバーにユーザー毎の認証情報をヘッダー伝播することで、 MCP サーバーからデータ基盤にアクセスする際にデータの FGAC を実現できることを解説した。
コンポーネント 役割 設計上のポイント AgentCore Gateway / Request Interceptor ID Token からセッションタグ付き ⼀時認証キーへの交換・ヘッダー伝播 Credential Vending を担う。 同⼀ Interceptor を複数 MCP サーバーに再利⽤可能 MCP Server (AgentCore Runtime) ⼀時認証キーでユーザーの代理として データ基盤にクエリ実⾏ on behalf of パターン。 テナント判別ロジック不要でデータアクセスに専念 バックエンド (Lake Formation) Cedar ポリシーでセッションタグを評価 しテナント毎のアクセス制御 最⼩権限の原則で、DB・テーブル・⾏レベルの FGAC をバックエンドに委譲 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 46 -
より Dive Deep したい⽅は AWS Japan の Zenn にて、検証記事や CDK
の実装を公開しているので、ぜひご覧下さい。 https://zenn.dev/aws_japan/articles/004-bedrock-agentcore-fgac-multitenant-isolation © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. https://zenn.dev/aws_japan/articles/003-bedrock-agentcore-policy-fgac 47 -
Thank you! Renya Kujirada X: @recat_125 © 2026, Amazon Web
Services, Inc. or its affiliates. All rights reserved. © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved.
 ren8k
 silmin_
 mikanichinose
 yusuke427
 imuta
 ymotongpoo
 jcabot
 yappli_developers
 ykimi
 kasada
 ama_ch
 kazzpapa3
 wind111
 cromwellryan
 bluesmoon
 addyosmani
 katarinadahlin
 honnibal
 ipullrank
 shpigford
 katiecoart
 danielanewman
 kimpetersen
 cargoodrich