Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Introduction à Kubernetes
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Renaud Chaput
October 23, 2017
Technology
460
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Introduction à Kubernetes
Présenté à Sysadmin Days #7 :
https://sysadmindays.fr
Renaud Chaput
October 23, 2017
More Decks by Renaud Chaput
See All by Renaud Chaput
L'Infrastructure as Code au complet (par Benoit Petit)
renchap
1
730
Autour des requêtes des TSDB
renchap
2
740
Operate HBase clusters at Scale
renchap
1
470
Versions (par Olivier Delhomme)
renchap
1
500
Prevent business logic attacks using dynamic instrumentation
renchap
1
490
Atelier Paris Web : Introduction à Docker
renchap
0
120
Alkemics CI & CD with Jenkins and Docker
renchap
1
350
Les containers : décryptage
renchap
2
340
Kubernetes en production : un an après
renchap
1
380
Other Decks in Technology
See All in Technology
go-sqletch
moznion
0
140
freeeらしさをAIとともに作る / Creating the freee Experience with AI
ymrl
0
230
[AWS 秋のクラウドオペレーション祭り 2026]AWS DevOps Agentで変わる リリースと運用対応 ~リリース管理機能と Directed actions のご紹介~
furuton
4
1.2k
実体験から学ぶ分析エージェントの開発と運⽤
recruitengineers
PRO
8
2.2k
契約書画像からの情報抽出に特化した視覚接地モデルを育てる話
sansantech
PRO
1
170
TinyGoでオブザーバビリティ?OpenTelemetryはTinyGoで使えるのか / Is OpenTelemetry available in TinyGo environment?
ymotongpoo
2
140
事業活動を AI Ready にする攻めと守りのデータエンジニアリング / data-engineering-for-ai-ready-business
pei0804
7
2.6k
WasmをRustにする
sansantech
PRO
0
190
DevelopersIO 2026 知識の地図を描く ─ オントロジーとは何か?
ishikawa_satoru
1
1.5k
生成AIと進める探索的データ分析(2026.10.03 第122回Tokyo.R勉強会)
tatamiya
2
1.5k
DWH の限界突破! AI エージェント向け爆速リアルタイムデータ基盤 ClickHouse
jozono
1
390
"優秀な誰か"の下位互換にならないために
yut0naga1_fa
1
1.7k
Featured
See All Featured
Why Our Code Smells
bkeepers
PRO
340
58k
The AI Search Optimization Roadmap by Aleyda Solis
aleyda
2
6.3k
Introduction to Domain-Driven Design and Collaborative software design
baasie
1
1k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
[Rails World 2026] Durable orchestration on Rails: from continuation to workflow
palkan
1
730
世界の人気アプリ100個を分析して見えたペイウォール設計の心得
akihiro_kokubo
PRO
74
43k
A brief & incomplete history of UX Design for the World Wide Web: 1989–2019
jct
2
530
YesSQL, Process and Tooling at Scale
rocio
174
15k
Optimizing for Happiness
mojombo
378
71k
[Rails World 2023 - Day 1 Closing Keynote] - The Magic of Rails
eileencodes
38
3.1k
The Success of Rails: Ensuring Growth for the Next 100 Years
eileencodes
47
8.4k
Lessons Learnt from Crawling 1000+ Websites
charlesmeaden
PRO
1
1.6k
Transcript
Introduction à Kubernetes
Renaud Chaput @renchap
Kubernetes
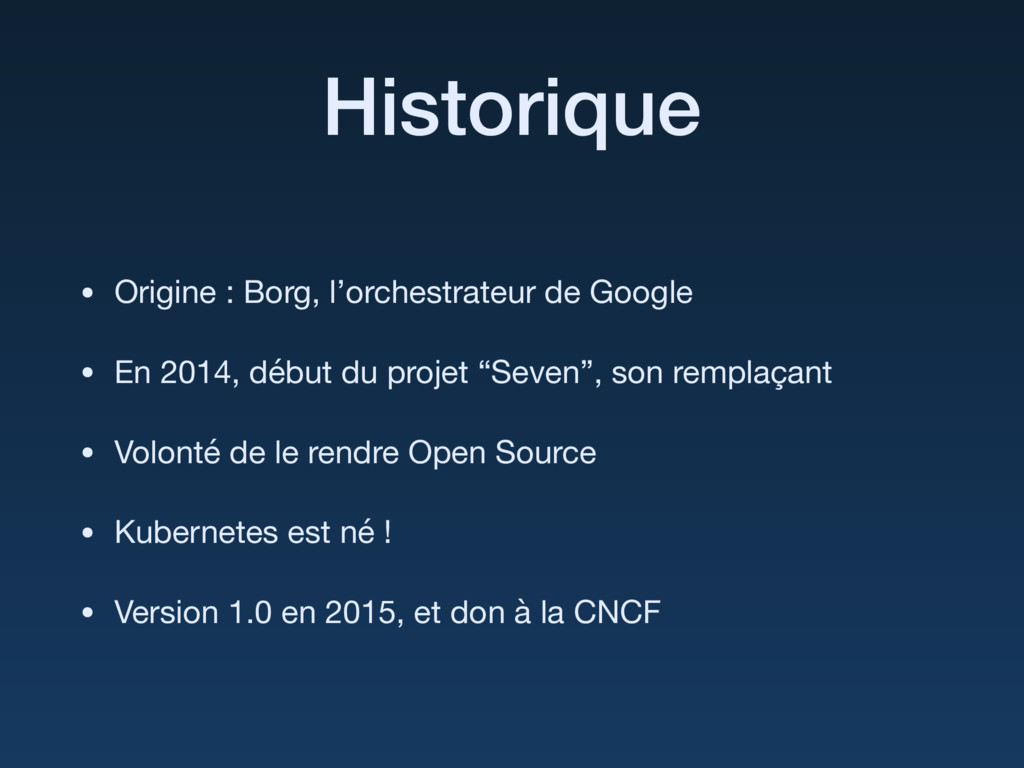
Historique • Origine : Borg, l’orchestrateur de Google • En
2014, début du projet “Seven”, son remplaçant • Volonté de le rendre Open Source • Kubernetes est né ! • Version 1.0 en 2015, et don à la CNCF
Objectifs • Découpler infra et applications • Scale • Générique
/ Flexible • Automatisable • Extensible • Portable (cloud provider, bare metal, …)
Un gros projet 1500 contributeurs 32 000 PR depuis 2014
Structure • Code of Conduct et CLA • Doc claire
sur la participation • Special Interest Groups (SIGs) • Working groups • Committees
Releases
Releases
Features Alpha 1.5 Décembre 2016 Beta 1.7 Juin 2017 Stable
1.8 Septembre 2017 Alpha 1.6 Mars 2017
Fonctionnement
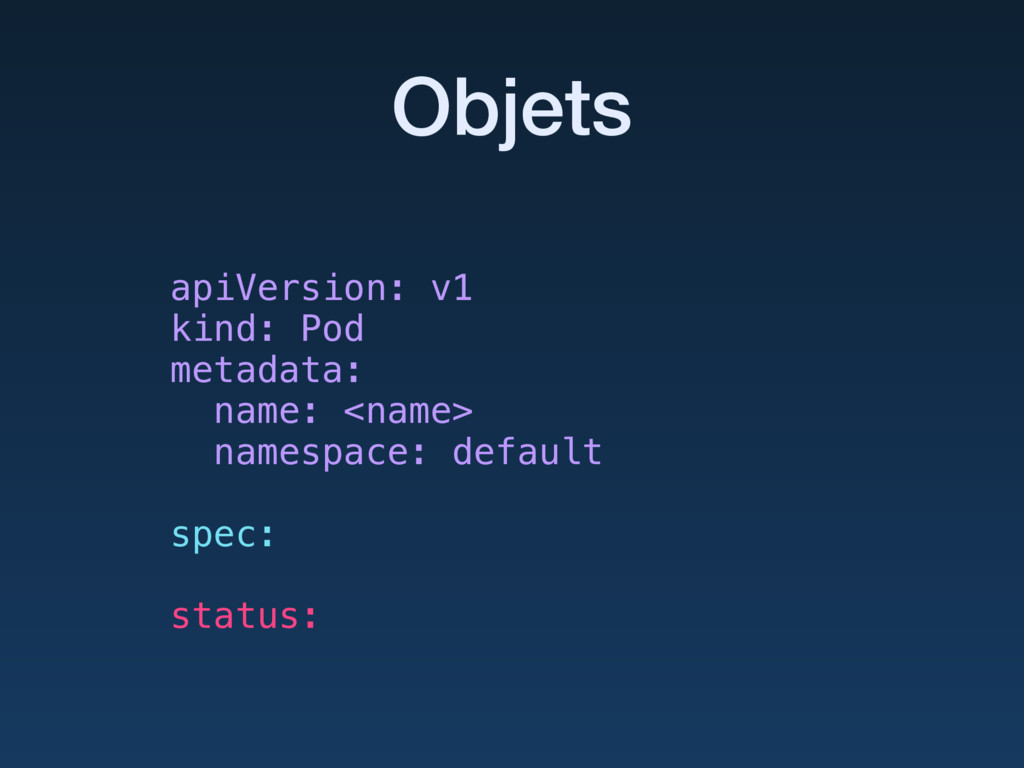
Objets apiVersion: v1 kind: Pod metadata: name: <name> namespace: default
spec: status:
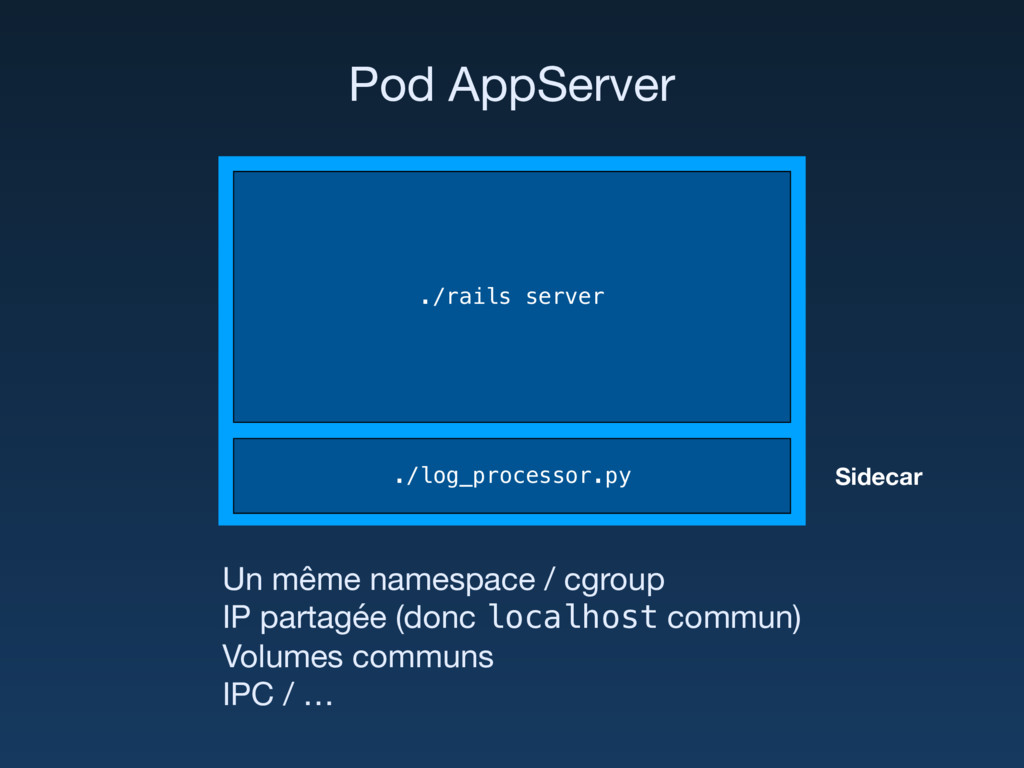
Un même namespace / cgroup IP partagée (donc localhost commun)
Volumes communs IPC / … ./rails server ./log_processor.py Pod AppServer Sidecar
apiVersion: v1 kind: Pod metadata: name: nginx spec: containers: -
name: nginx image: nginx:1.7.9 ports: - containerPort: 8080 Pod simple
Deployment apiVersion: apps/v1beta2 kind: Deployment metadata: name: nginx-deployment labels: app:
nginx spec: replicas: 3 selector: matchLabels: app: nginx template: metadata: labels: app: nginx spec: containers: - name: nginx image: nginx:1.7.9 ports: - containerPort: 8080
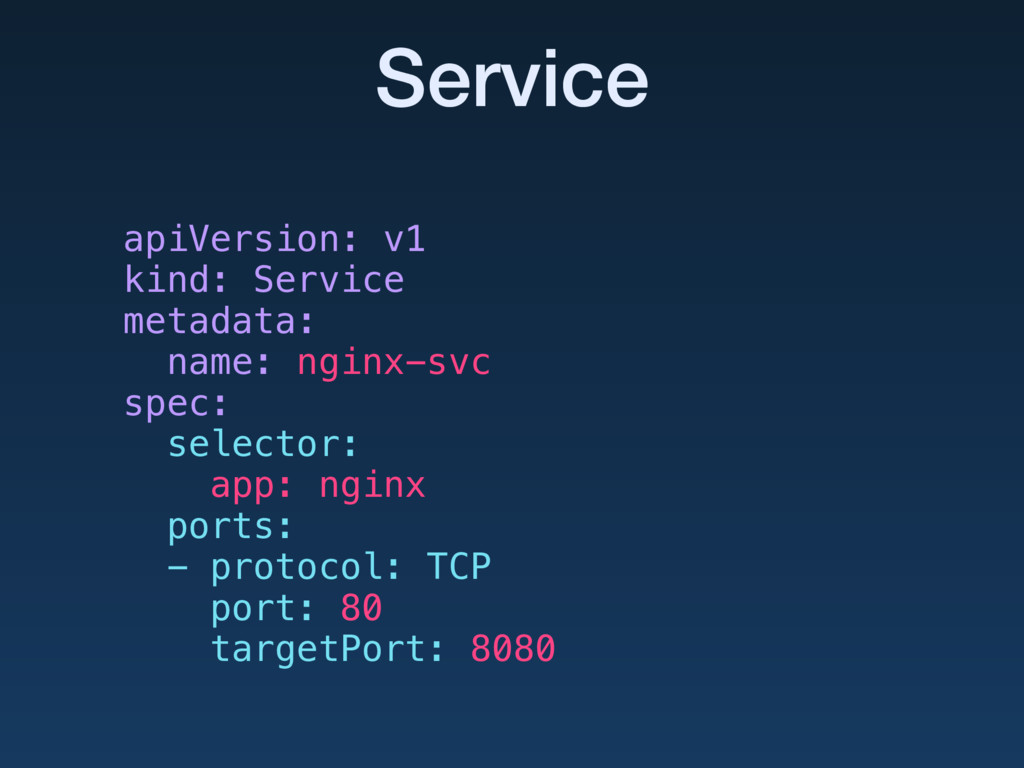
Service apiVersion: v1 kind: Service metadata: name: nginx-svc spec: selector:
app: nginx ports: - protocol: TCP port: 80 targetPort: 8080
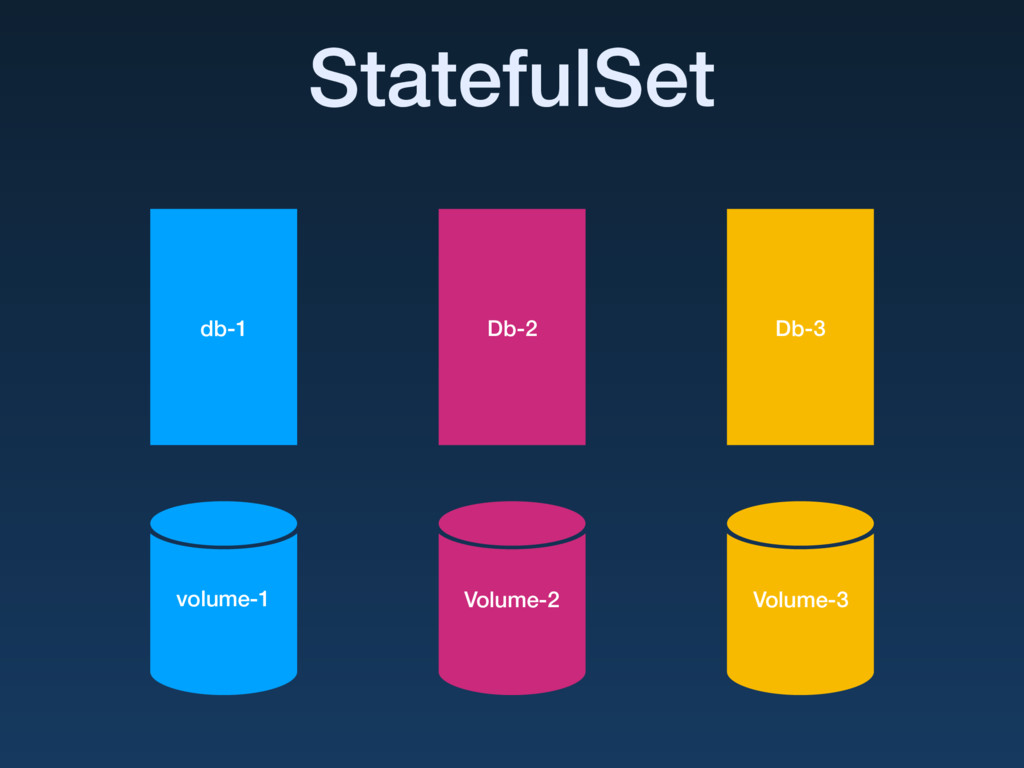
db-1 volume-1 StatefulSet Db-2 Volume-2 Db-3 Volume-3
DaemonSet Jobs CronJobs NetworkPolicy Secret Ingress Volume …
Architecture
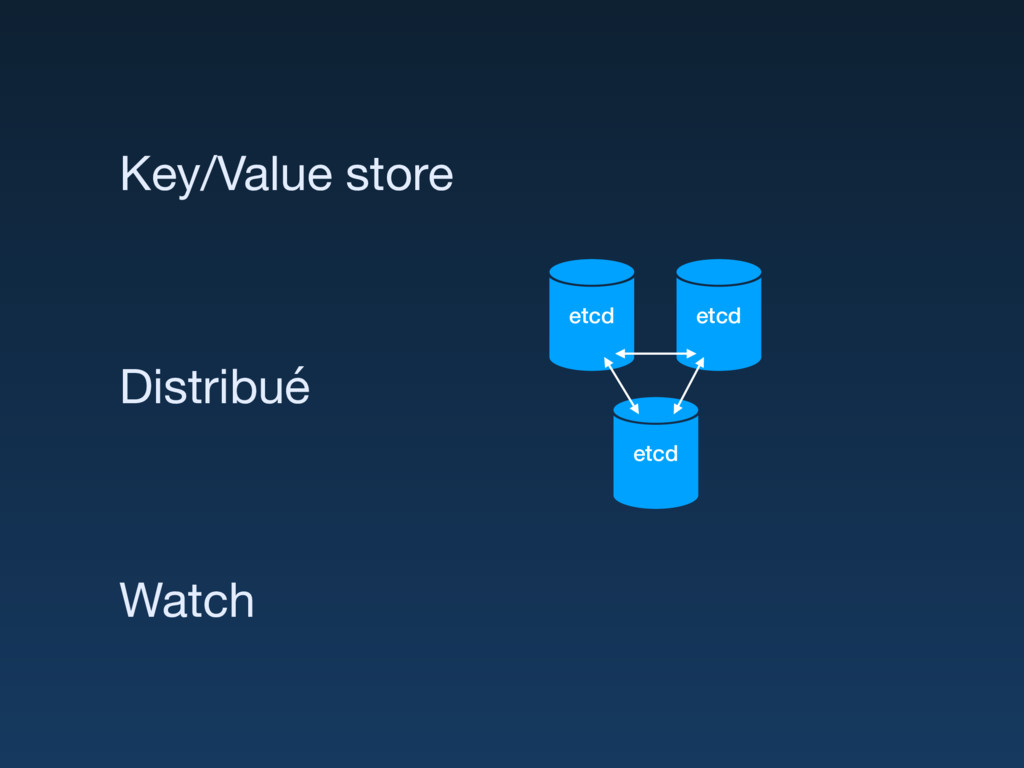
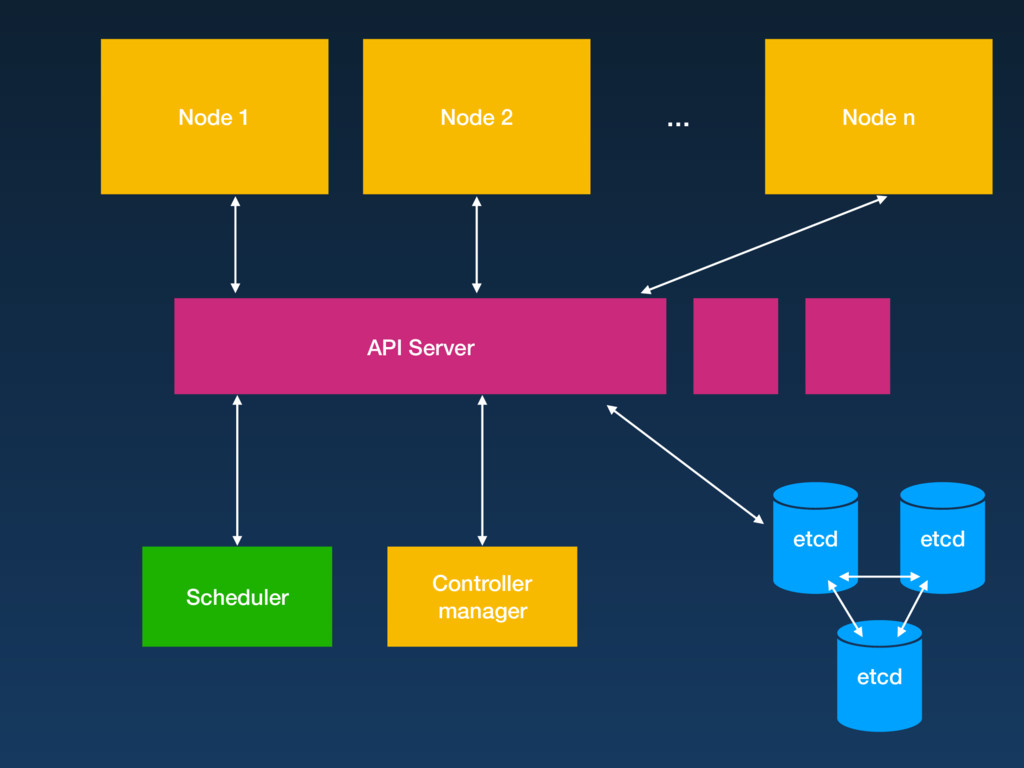
etcd etcd etcd Key/Value store Distribué Watch
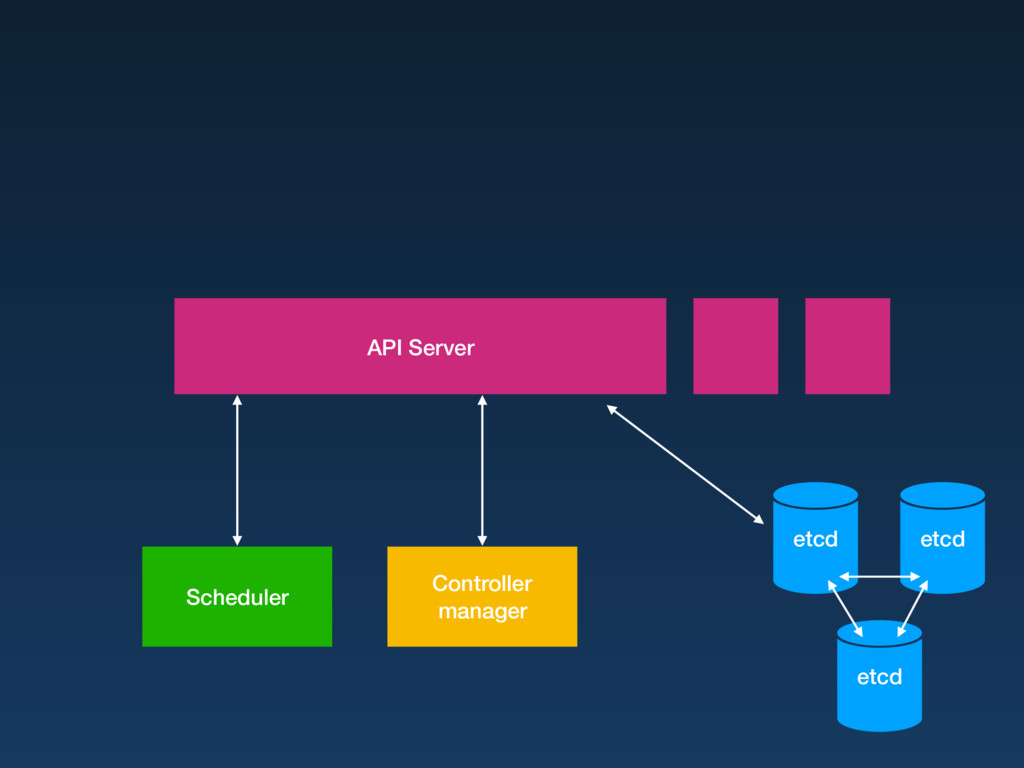
etcd etcd etcd API Server Scheduler Controller manager
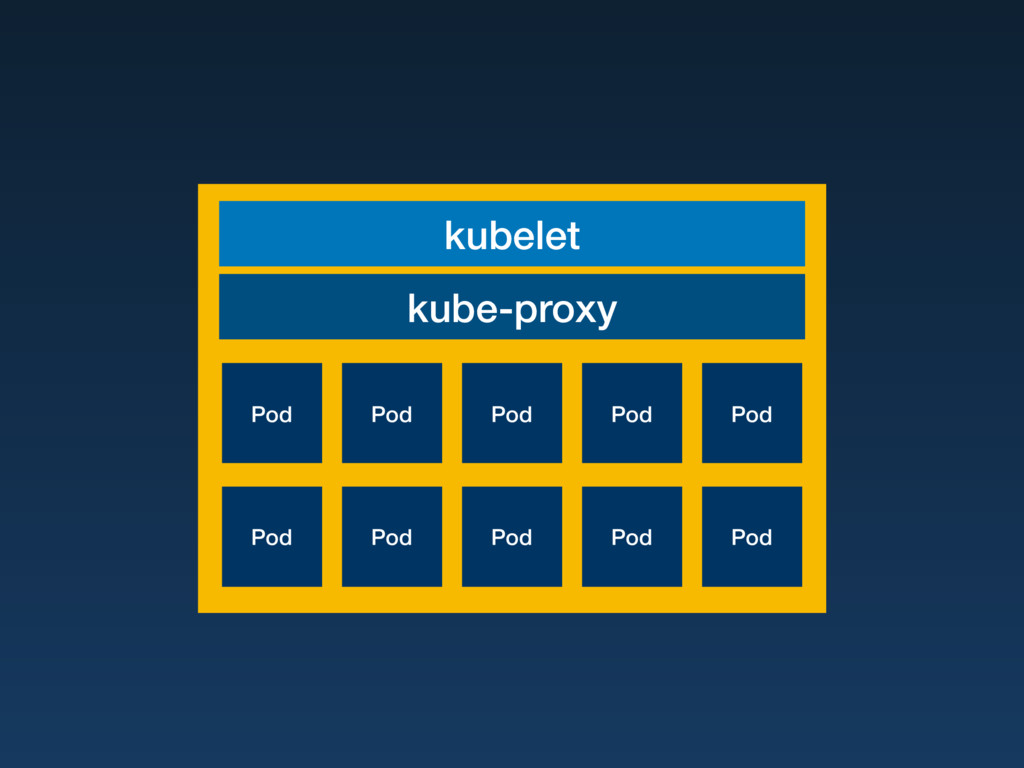
kubelet kube-proxy Pod Pod Pod Pod Pod Pod Pod Pod
Pod Pod
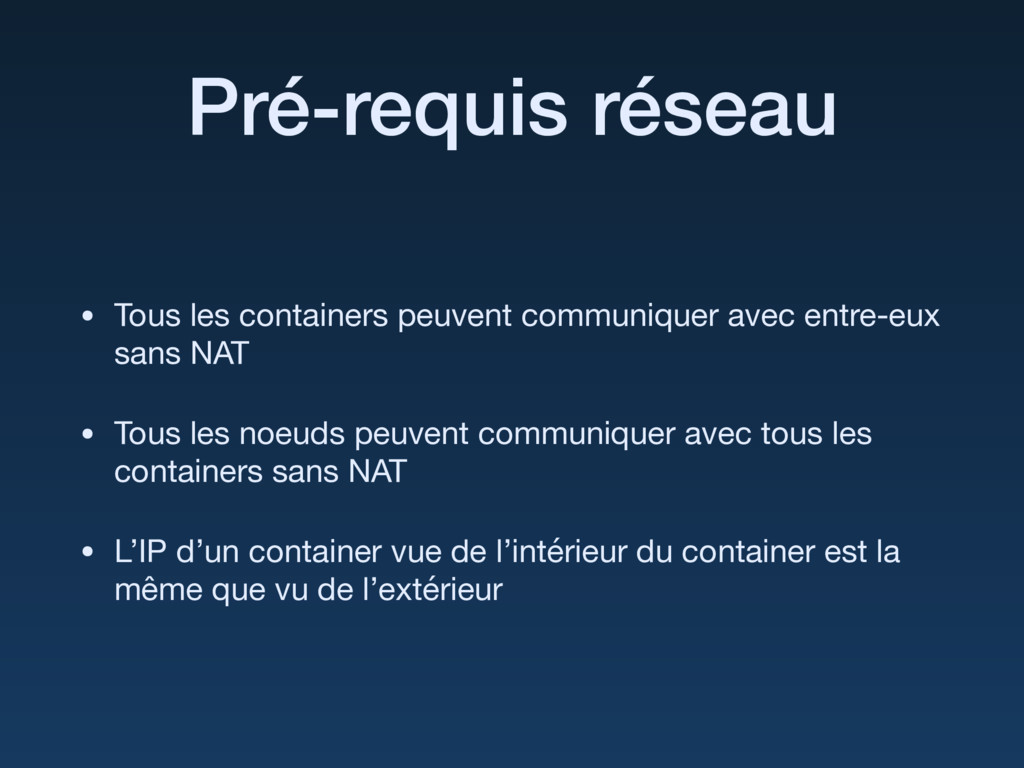
Pré-requis réseau • Tous les containers peuvent communiquer avec entre-eux
sans NAT • Tous les noeuds peuvent communiquer avec tous les containers sans NAT • L’IP d’un container vue de l’intérieur du container est la même que vu de l’extérieur
Container Runtime • Docker • CRI-O : interface OCI standard
• rkt (CoreOS) • Frakti : basé sur un hyperviseur
Node 1 Node 2 Node n etcd etcd etcd API
Server Scheduler Controller manager …
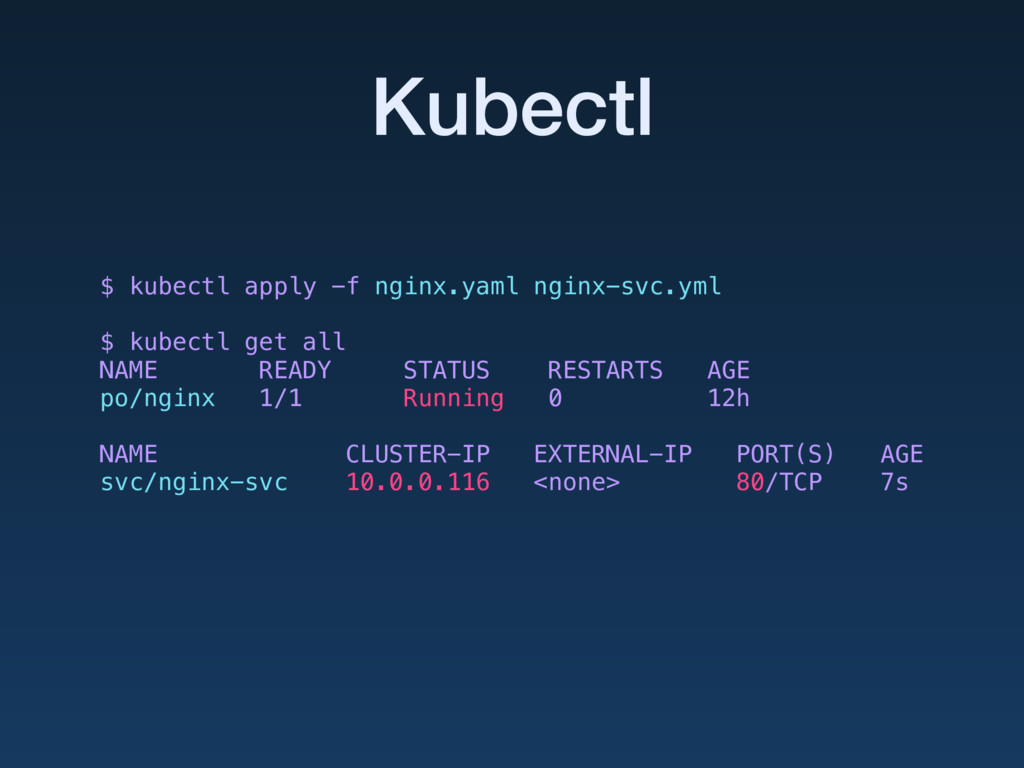
Kubectl $ kubectl apply -f nginx.yaml nginx-svc.yml $ kubectl get
all NAME READY STATUS RESTARTS AGE po/nginx 1/1 Running 0 12h NAME CLUSTER-IP EXTERNAL-IP PORT(S) AGE svc/nginx-svc 10.0.0.116 <none> 80/TCP 7s
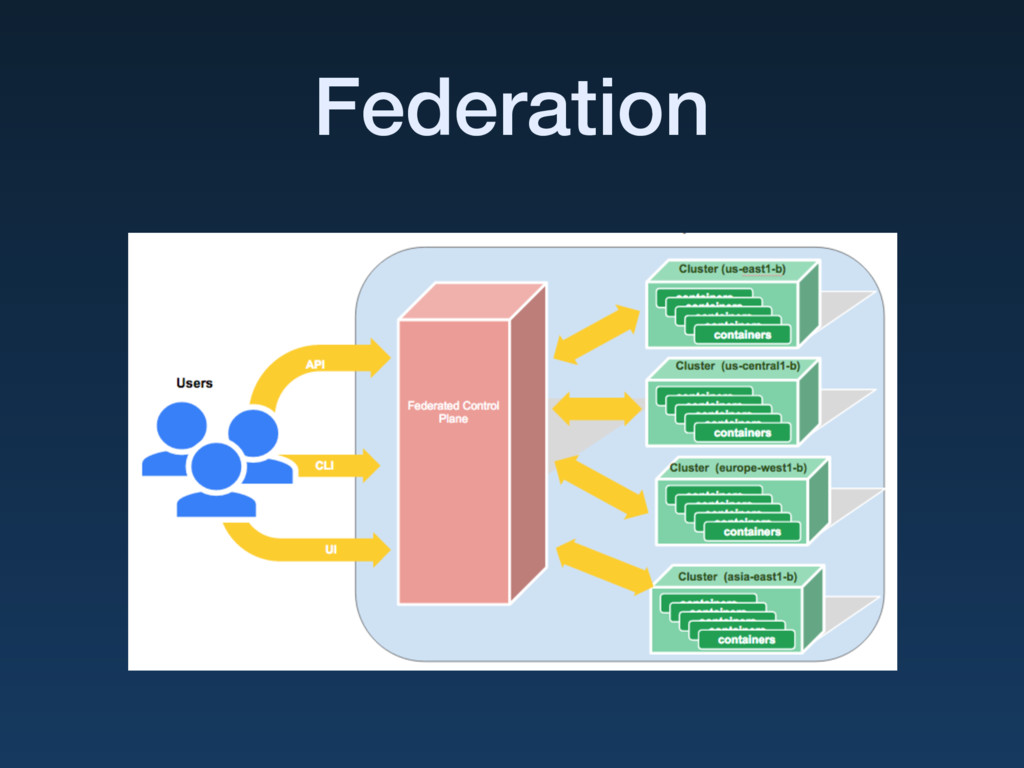
Federation
Add-ons
Kube DNS nginx-svc.my-namespace.svc.cluster.local _http._tcp.nginx-svc.my-namespace.svc.cluster.local 1-2-3-4.default.pod.cluster.local
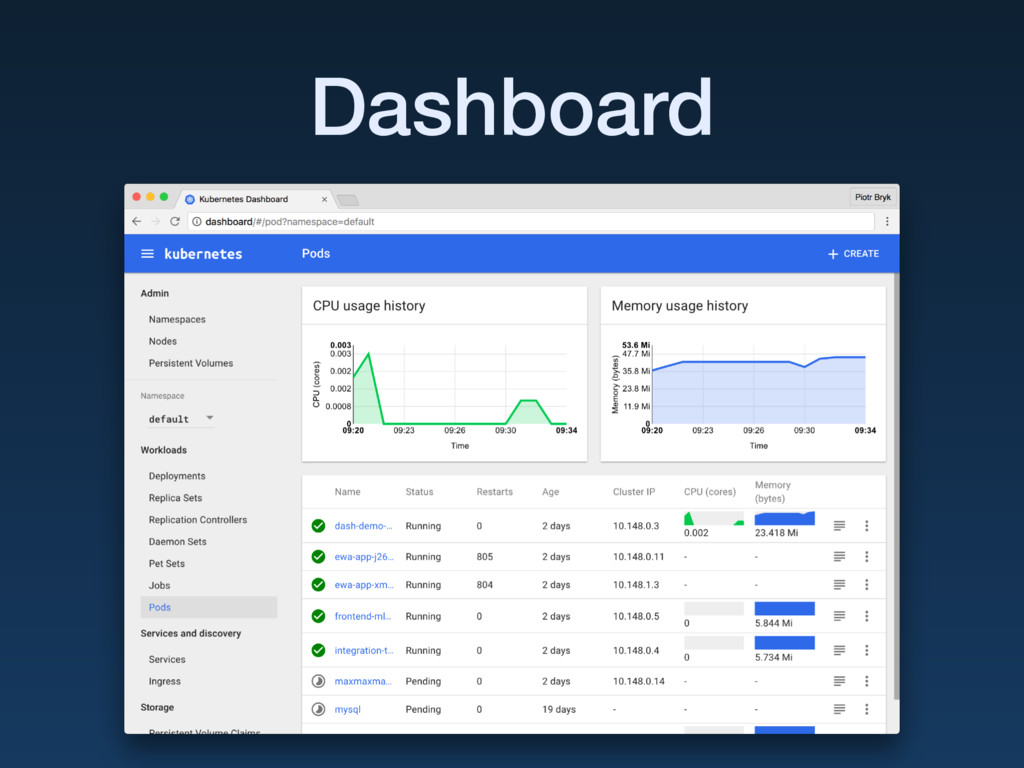
Dashboard
Ingress controllers • GCP / AWS / … • nginx
• haproxy
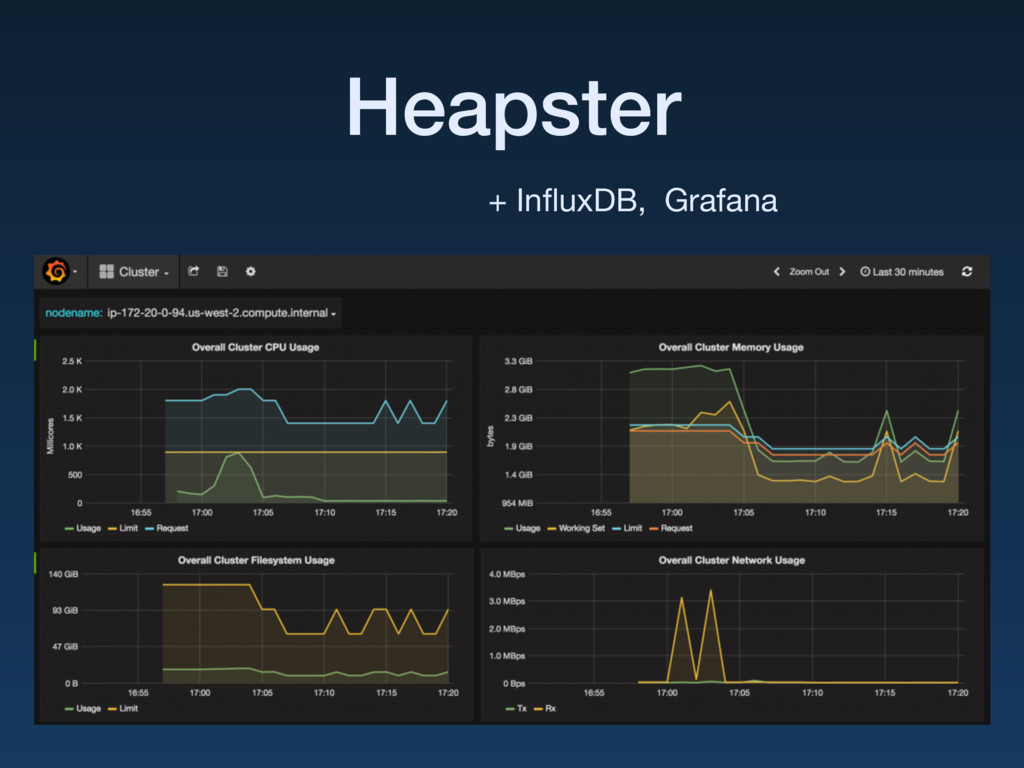
Heapster + InfluxDB, Grafana
Sécurité
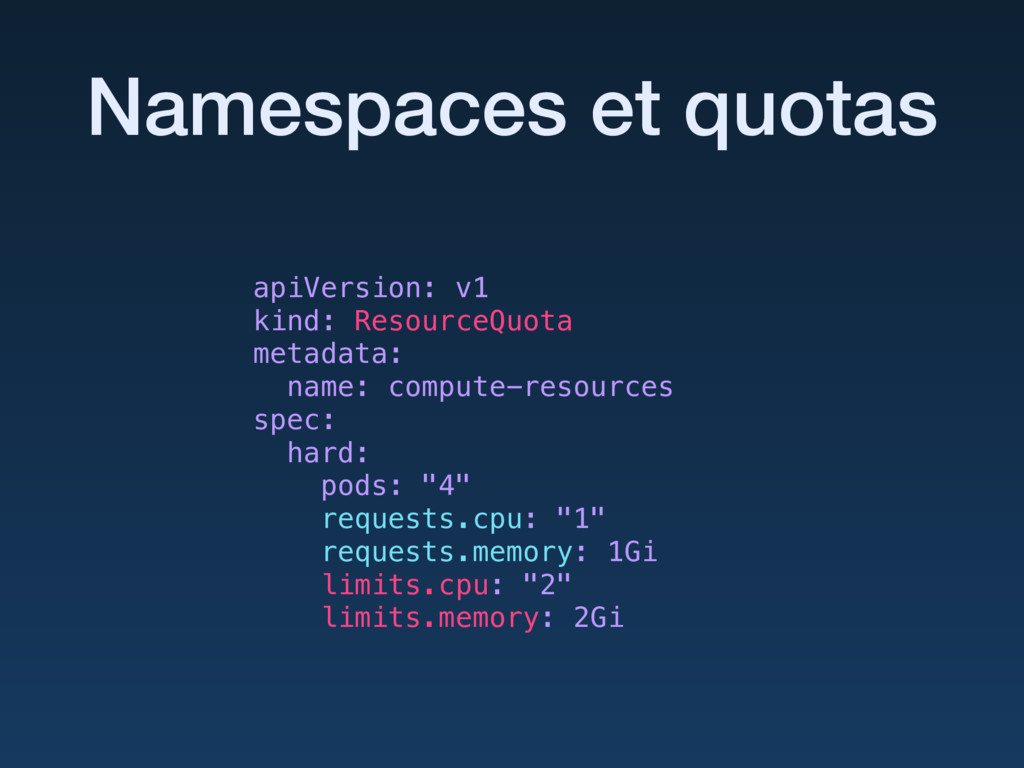
Namespaces et quotas apiVersion: v1 kind: ResourceQuota metadata: name: compute-resources
spec: hard: pods: "4" requests.cpu: "1" requests.memory: 1Gi limits.cpu: "2" limits.memory: 2Gi
PodSecurityPolicy apiVersion: extensions/v1beta1 kind: PodSecurityPolicy metadata: name: permissive spec: seLinux:
rule: RunAsAny supplementalGroups: rule: RunAsAny runAsUser: rule: RunAsAny fsGroup: rule: RunAsAny hostPorts: - min: 8000 max: 8080 volumes: - '*' allowedCapabilities: - '*'
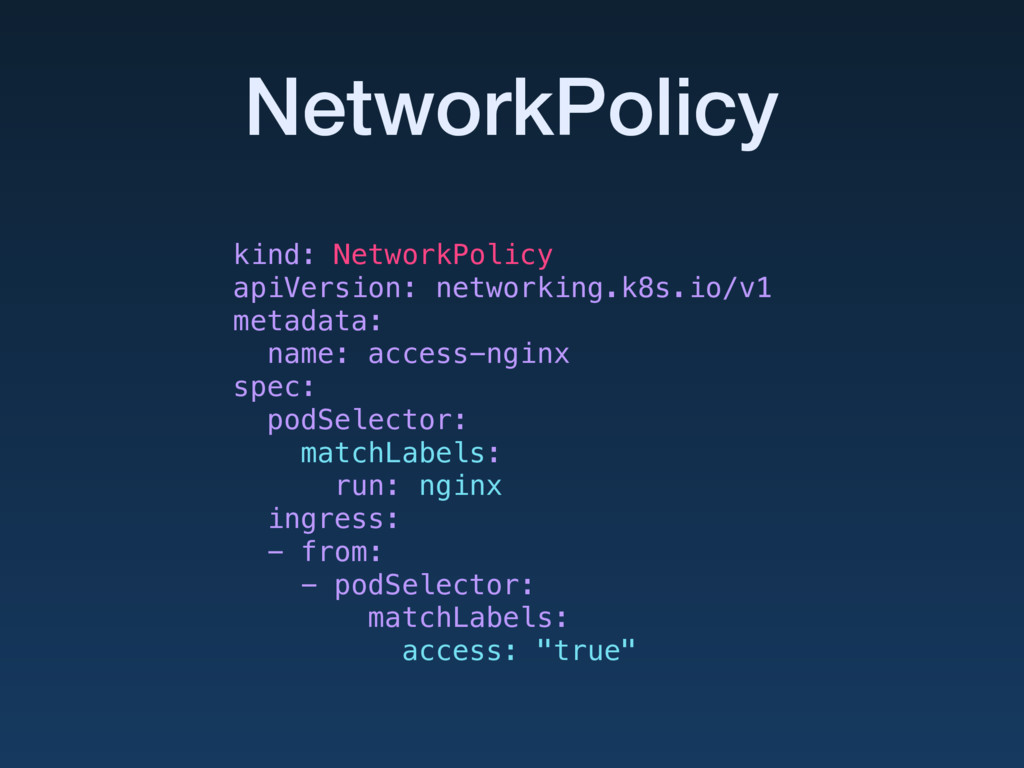
NetworkPolicy kind: NetworkPolicy apiVersion: networking.k8s.io/v1 metadata: name: access-nginx spec: podSelector:
matchLabels: run: nginx ingress: - from: - podSelector: matchLabels: access: "true"
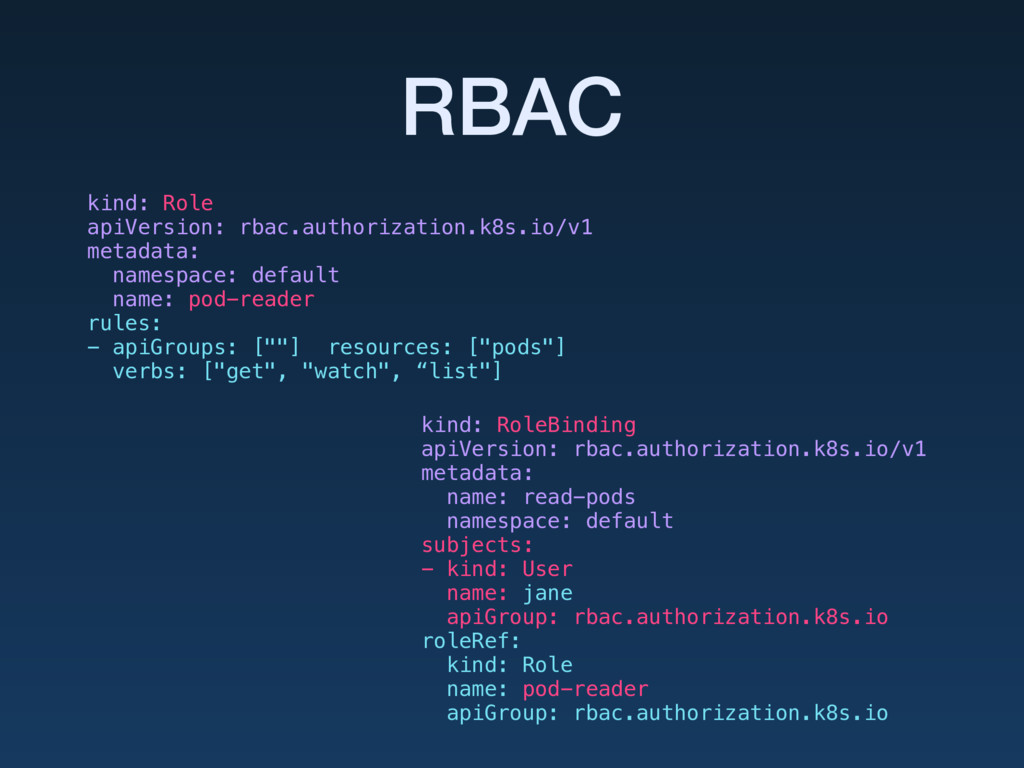
RBAC kind: Role apiVersion: rbac.authorization.k8s.io/v1 metadata: namespace: default name: pod-reader
rules: - apiGroups: [""] resources: ["pods"] verbs: ["get", "watch", “list"] kind: RoleBinding apiVersion: rbac.authorization.k8s.io/v1 metadata: name: read-pods namespace: default subjects: - kind: User name: jane apiGroup: rbac.authorization.k8s.io roleRef: kind: Role name: pod-reader apiGroup: rbac.authorization.k8s.io
Projets autour • Helm • Kops / Kube-AWS / Bootkube
/ … • Træfik • Prometheus / Sysdig / Datadog / … • Kube-lego, …
Ressources • Minikube! • kubernetes.io • Kubernetes the hard way
• Slack Kubernetes • Awesome Kubernetes
Questions ?


 renchap
 moznion
 ymrl
 furuton
 recruitengineers
 sansantech
 ymotongpoo
 pei0804
 ishikawa_satoru
 tatamiya
 jozono
 yut0naga1_fa
 bkeepers
 aleyda
 baasie
 destraynor
 palkan
 akihiro_kokubo
 jct
 rocio
 mojombo
 eileencodes
 charlesmeaden