Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
JAWS Pankration 2024 - Achieve software supply ...
Search
Richard Fan
August 25, 2024
Technology
87
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
JAWS Pankration 2024 - Achieve software supply chain security using AWS Nitro Enclaves and GitHub Actions
Presented at JAWS Pankration 2024
Richard Fan
August 25, 2024
More Decks by Richard Fan
See All by Richard Fan
Whose Fault When a Pentest Agent Attacks the Wrong Target
richardfan1126
0
39
You Don’t Need to Be a Hero to Contribute
richardfan1126
0
10
Understanding the Identity of a CI Platform
richardfan1126
0
18
Preserving privacy on data collaboration with AWS Clean Rooms
richardfan1126
0
55
Achieve software supply chain security using AWS Nitro Enclaves and GitHub Actions
richardfan1126
0
190
When Data Collaboration Meets Privacy: Privacy-enhancing Technologies on AWS
richardfan1126
0
68
AWS Security Hub Central Configuration - An Easy way to monitor your Organization security posture
richardfan1126
0
84
Create your first AWS Nitro Enclaves application
richardfan1126
0
85
Building Security Data Lake
richardfan1126
0
27
Other Decks in Technology
See All in Technology
PQC移行の今 -- IETF からみた現在地
satokan
4
500
Kiro Meetup #8 Kiro アップデート (2026/3/21〜2026/9/24)
katzueno
1
290
Amazon Bedrock Agents ClassicからAmazon Bedrock AgentCoreへ移行した際、ガードレール設定が2箇所に割れた話
matsunobu
0
130
Apache Iceberg が拓く AI 時代のオープンレイクハウス
tomtanaka
0
110
あけおめLINE 傾向とその対策
nasa9084
0
340
ADKで始める業務改善 - AIエージェント開発時の考えと設計
harappa80
2
300
技術的負債から考える、AI時代のエンジニアリング投資 — ビズリーチの技術的負債と向き合った経験から、変更し続けられるソフトウェアを考える/ technical-debt-con2026
visional_engineering_and_design
4
3.9k
GitHub Agentic Workflows を触ってみる
htkym
2
760
AIに任せた品質は、誰が見立てるのか - AI時代のテストマネジメント
nakanao
3
3.2k
いちAWSエンジニアのAI活用を振り返る #devio2026 / devio osaka 2026 kawahara
masahirokawahara
1
130
【ゲームメーカーズスクランブル2026】『Shadowverse: Worlds Beyond』UIとアニメーションで実現する最高のユーザー体験を叶えるプロトタイピング
cygames
PRO
1
630
Oracle Base Database Service 技術詳細
oracle4engineer
PRO
16
120k
Featured
See All Featured
4 Signs Your Business is Dying
shpigford
187
23k
Producing Creativity
orderedlist
PRO
348
41k
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
Six Lessons from altMBA
skipperchong
29
4.5k
Fashionably flexible responsive web design (full day workshop)
malarkey
409
67k
How to Think Like a Performance Engineer
csswizardry
28
2.8k
Ruling the World: When Life Gets Gamed
codingconduct
0
370
Building a Modern Day E-commerce SEO Strategy
aleyda
45
9.2k
BBQ
matthewcrist
89
10k
Odyssey Design
rkendrick25
PRO
2
820
Skip the Path - Find Your Career Trail
mkilby
1
240
Dealing with People You Can't Stand - Big Design 2015
cassininazir
367
27k
Transcript
Achieve software supply chain security using AWS Nitro Enclaves and
GitHub Actions Richard Fan AWS Security Hero
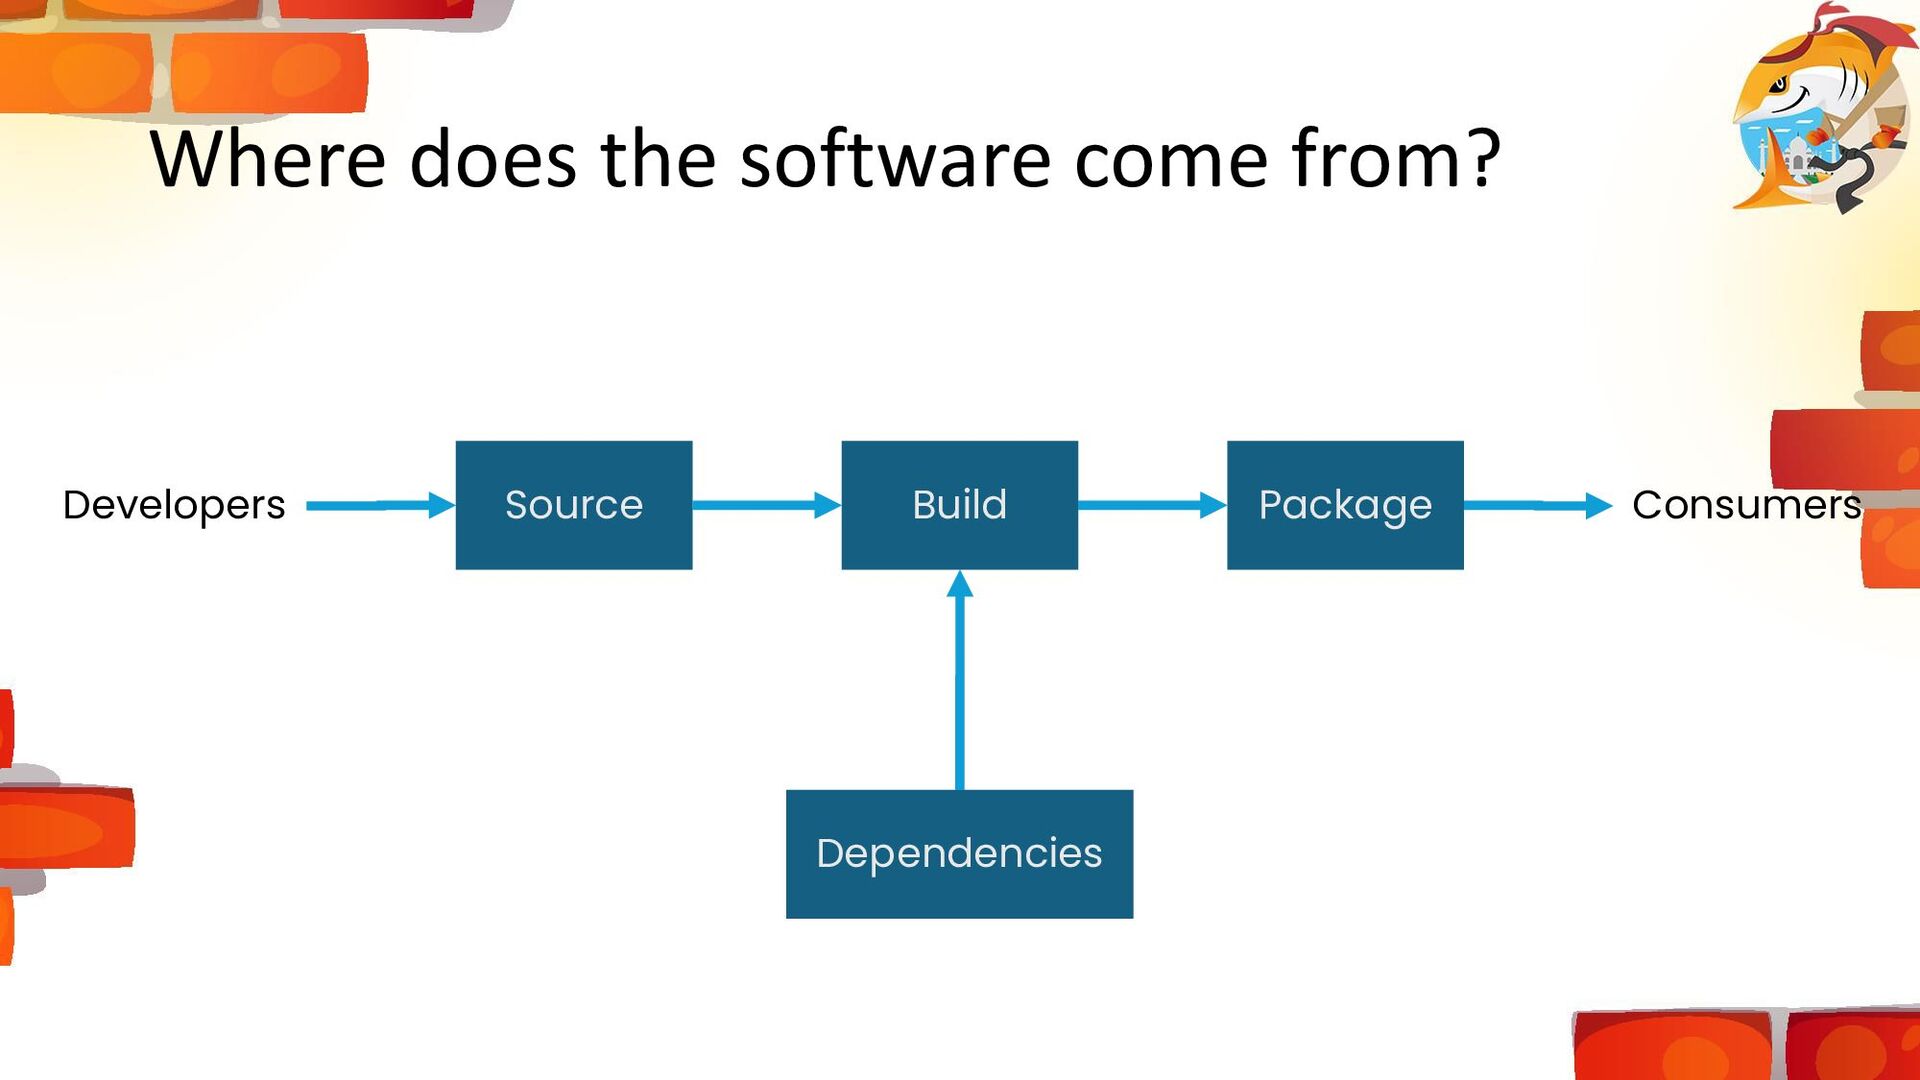
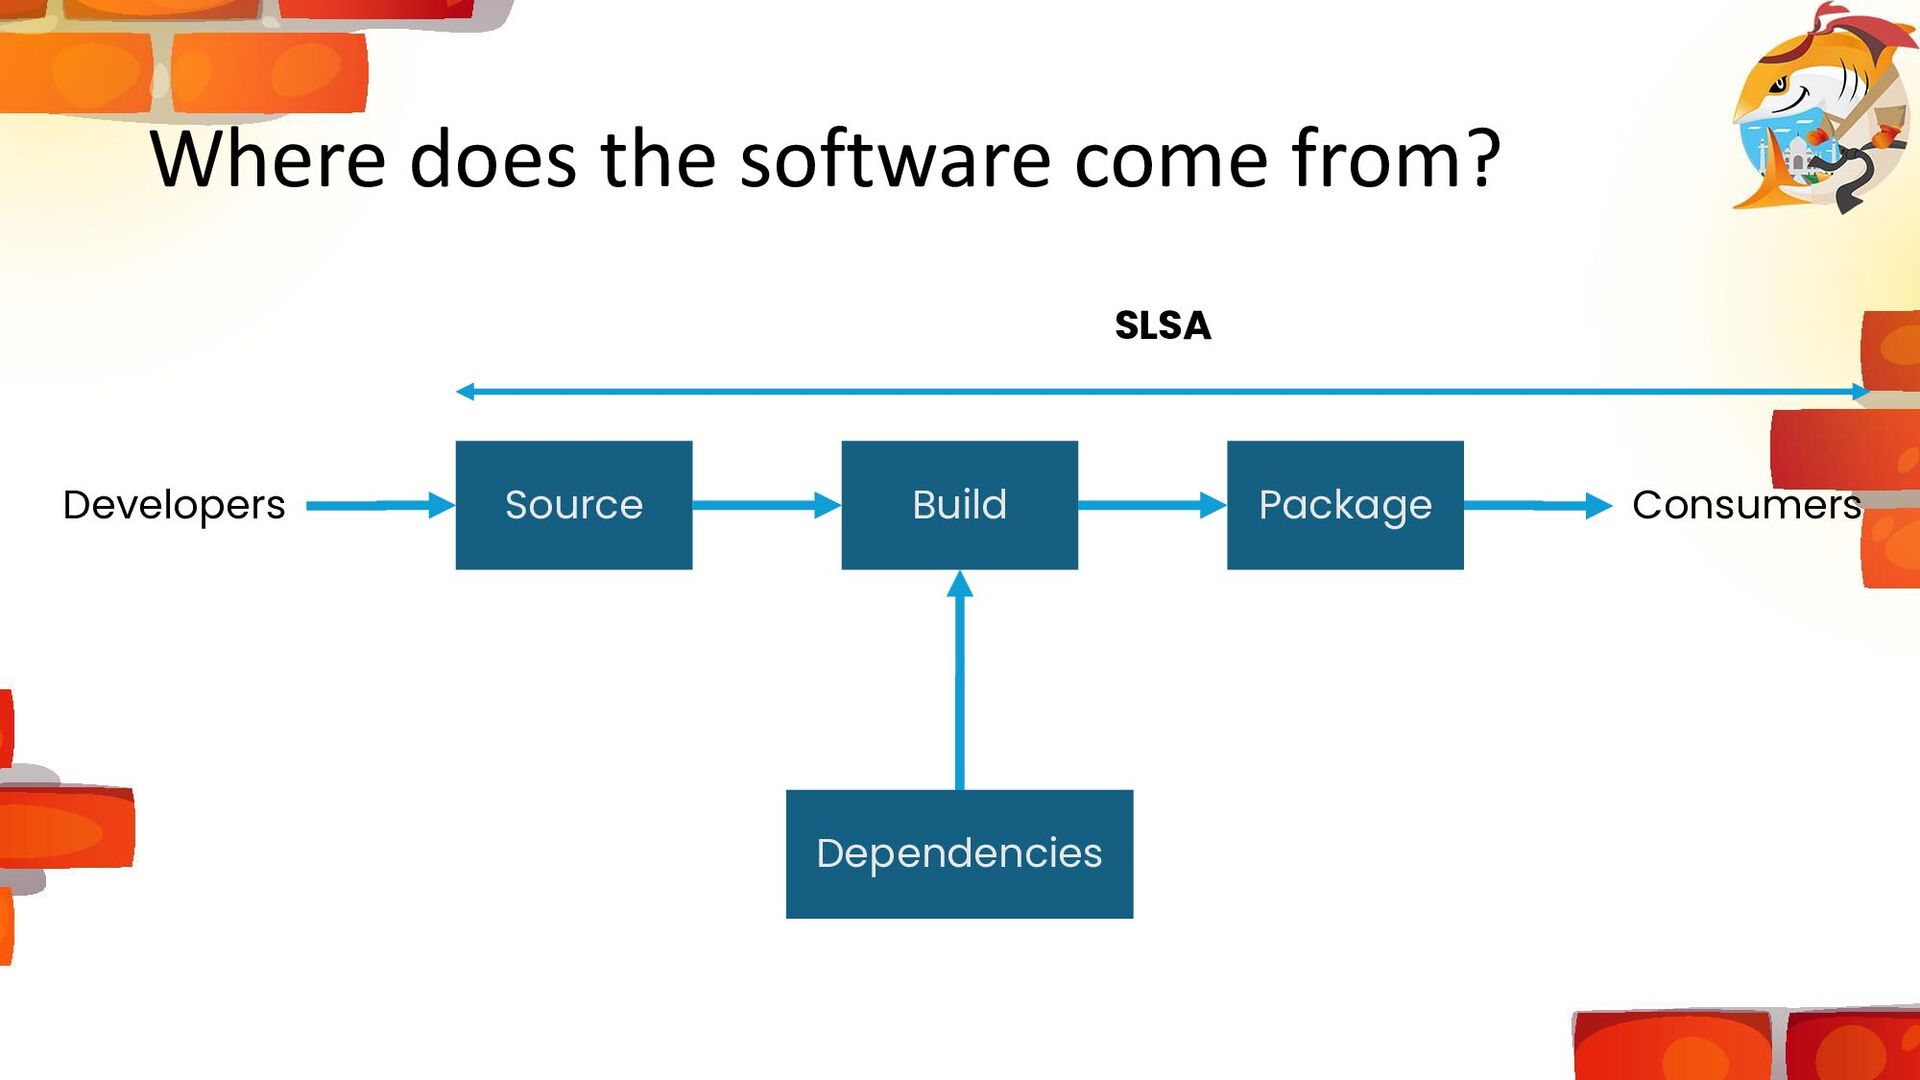
Where does the software come from? Source Developers Build Package
Consumers Dependencies
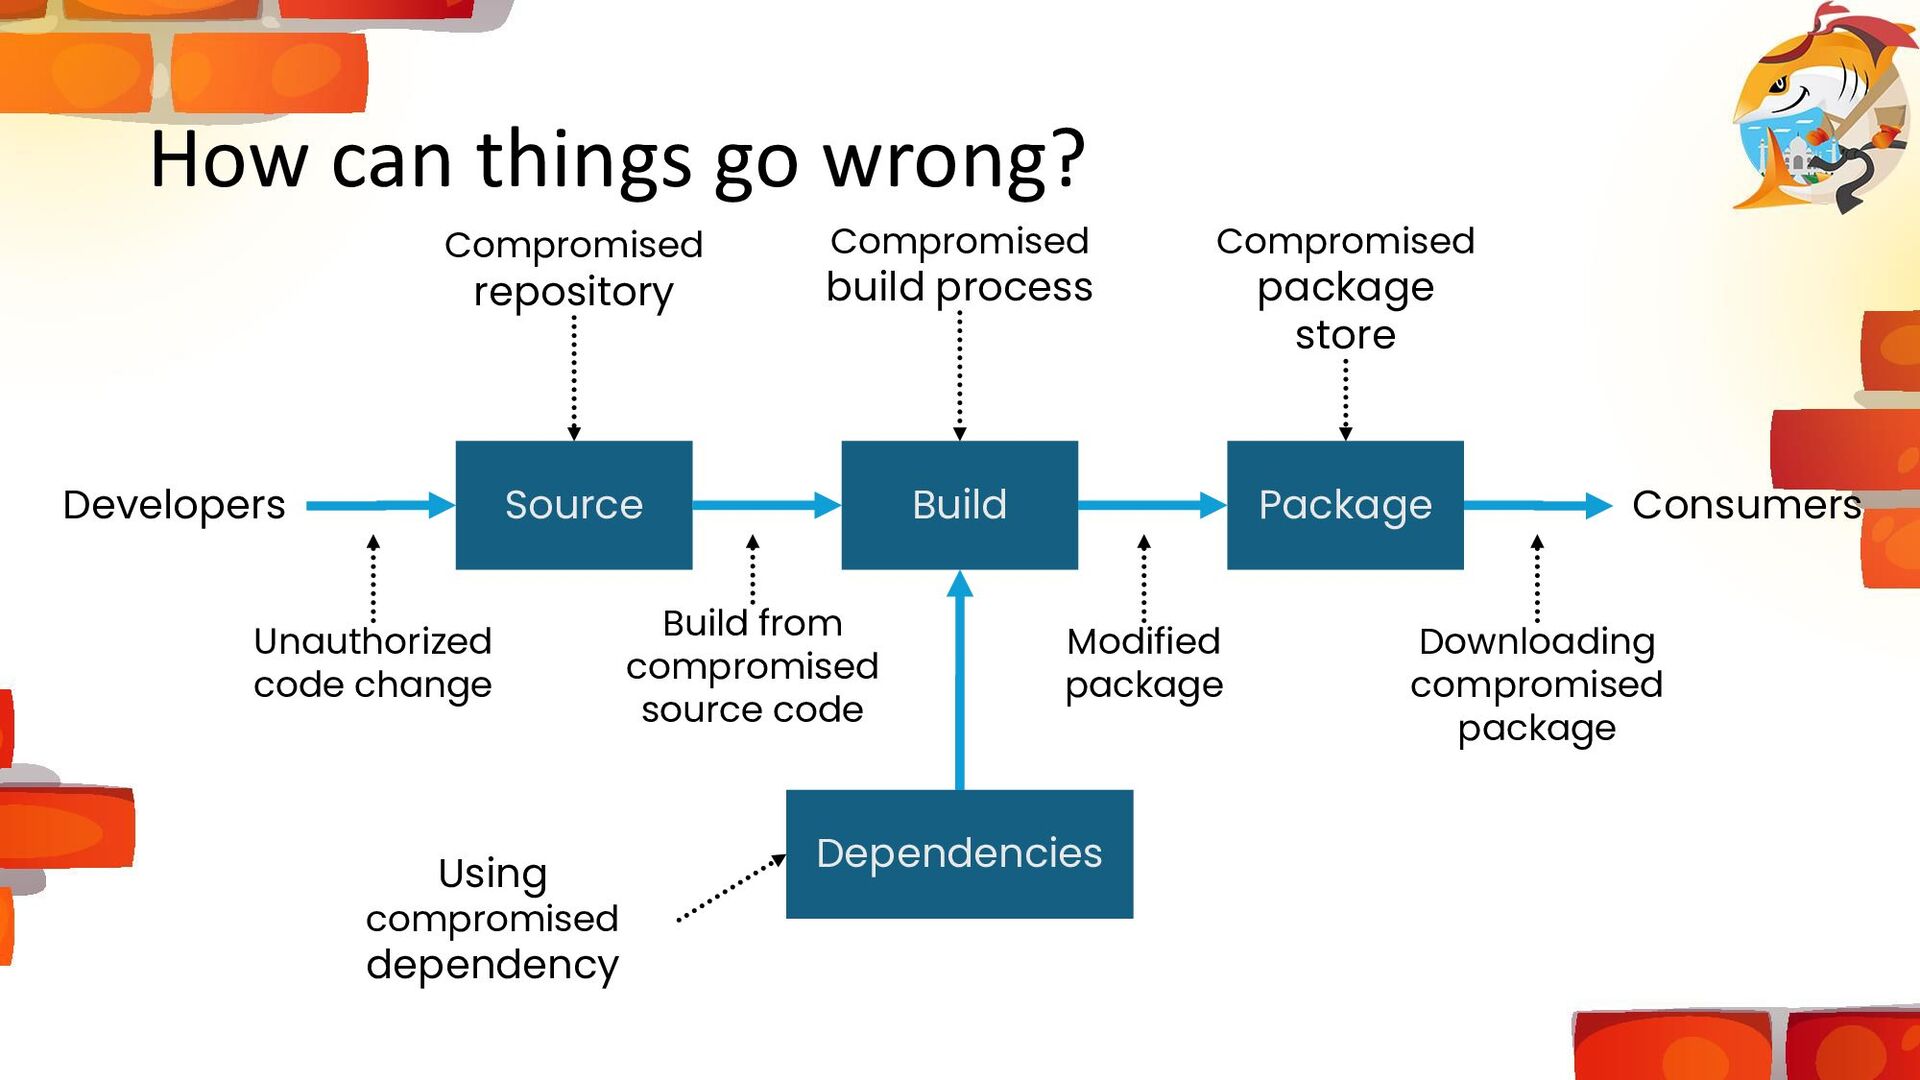
How can things go wrong? Source Developers Build Package Consumers
Dependencies Unauthorized code change Compromised repository Build from compromised source code Compromised build process Using compromised dependency Modified package Compromised package store Downloading compromised package
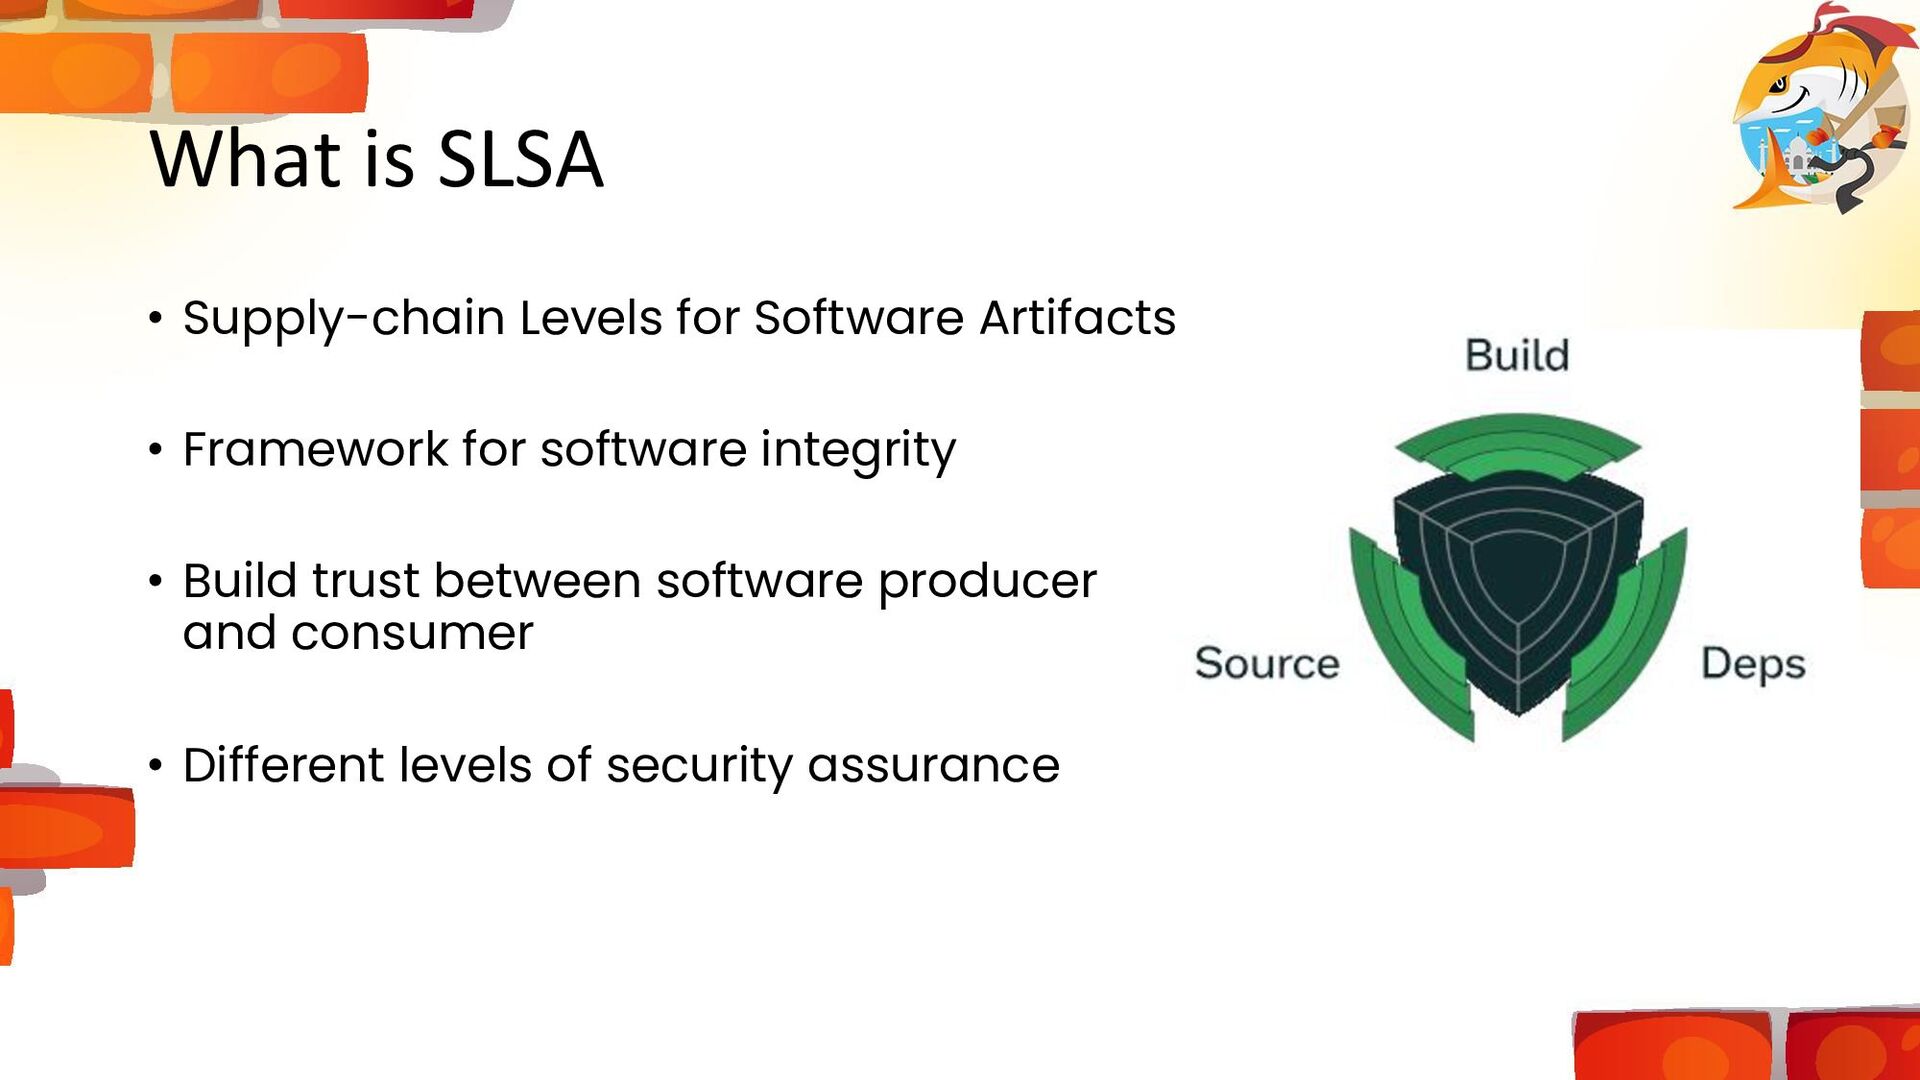
What is SLSA • Supply-chain Levels for Software Artifacts •
Framework for software integrity • Build trust between software producer and consumer • Different levels of security assurance
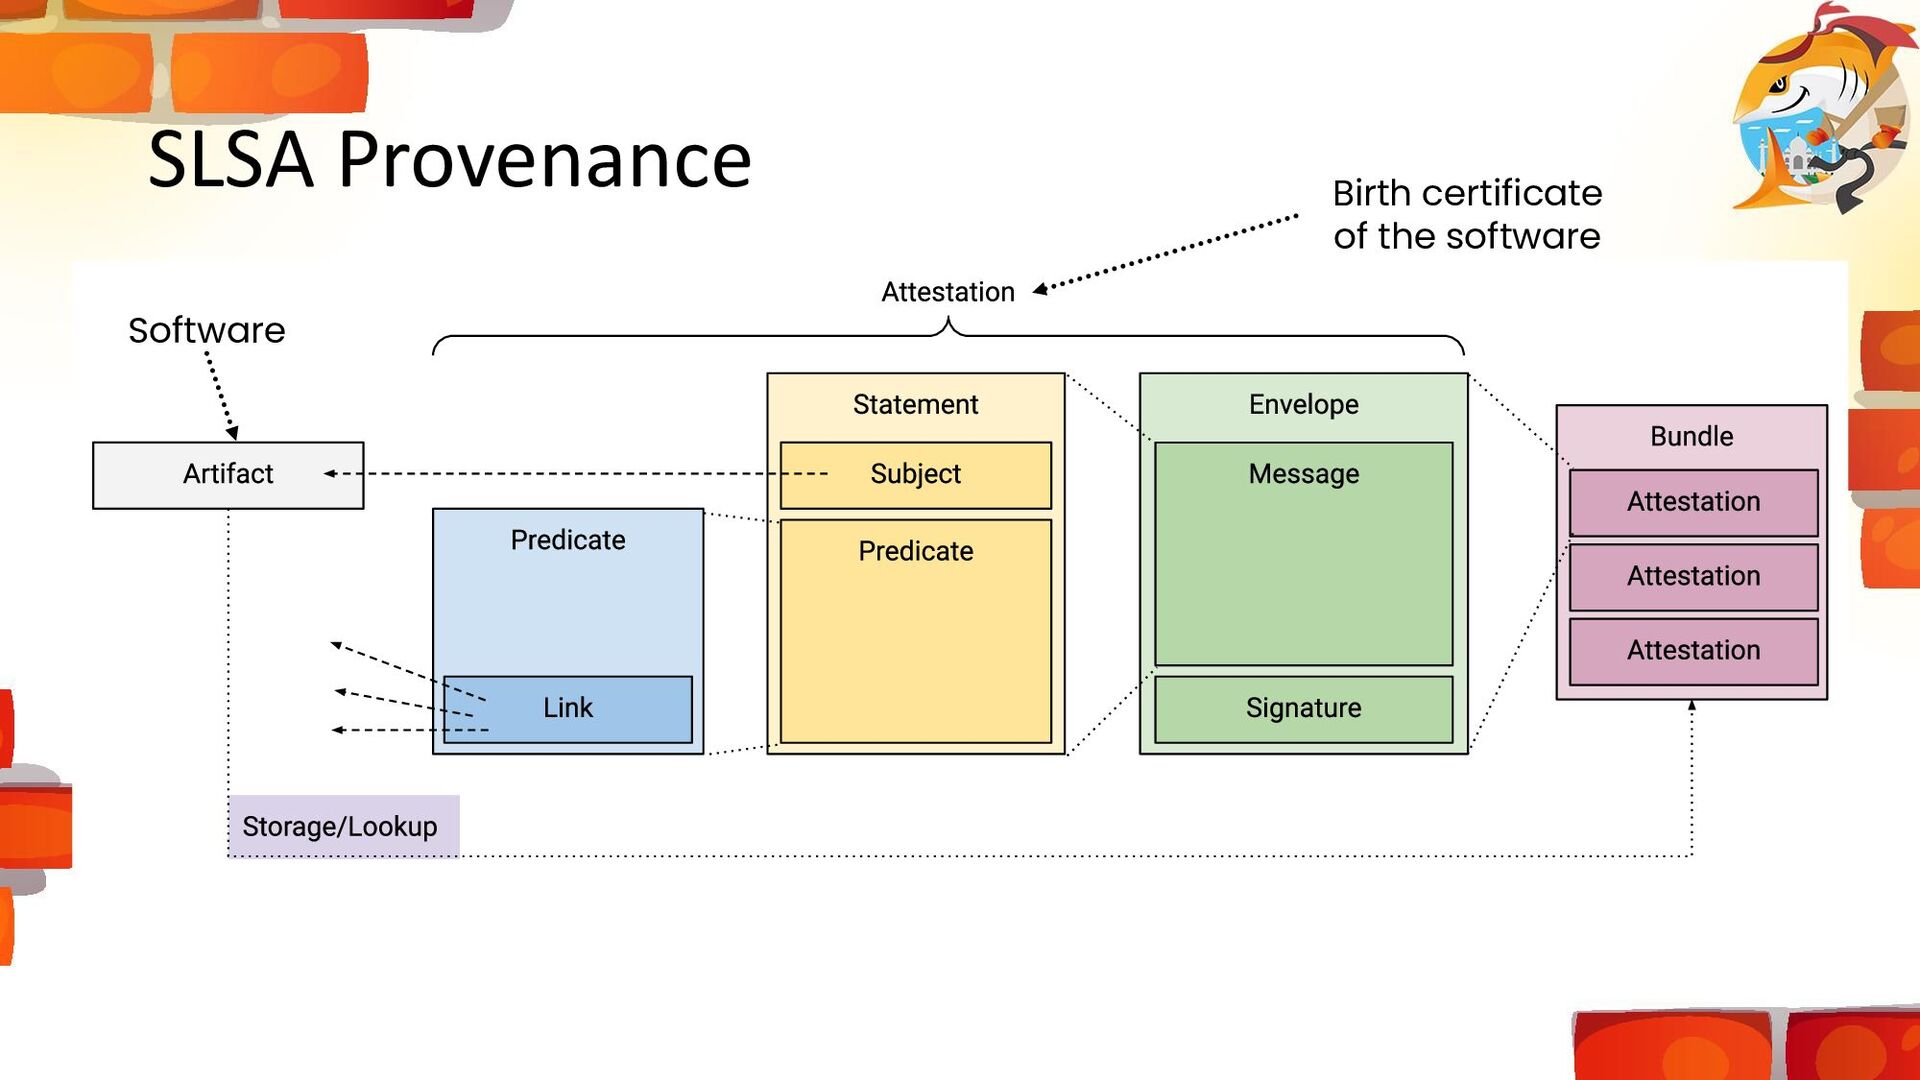
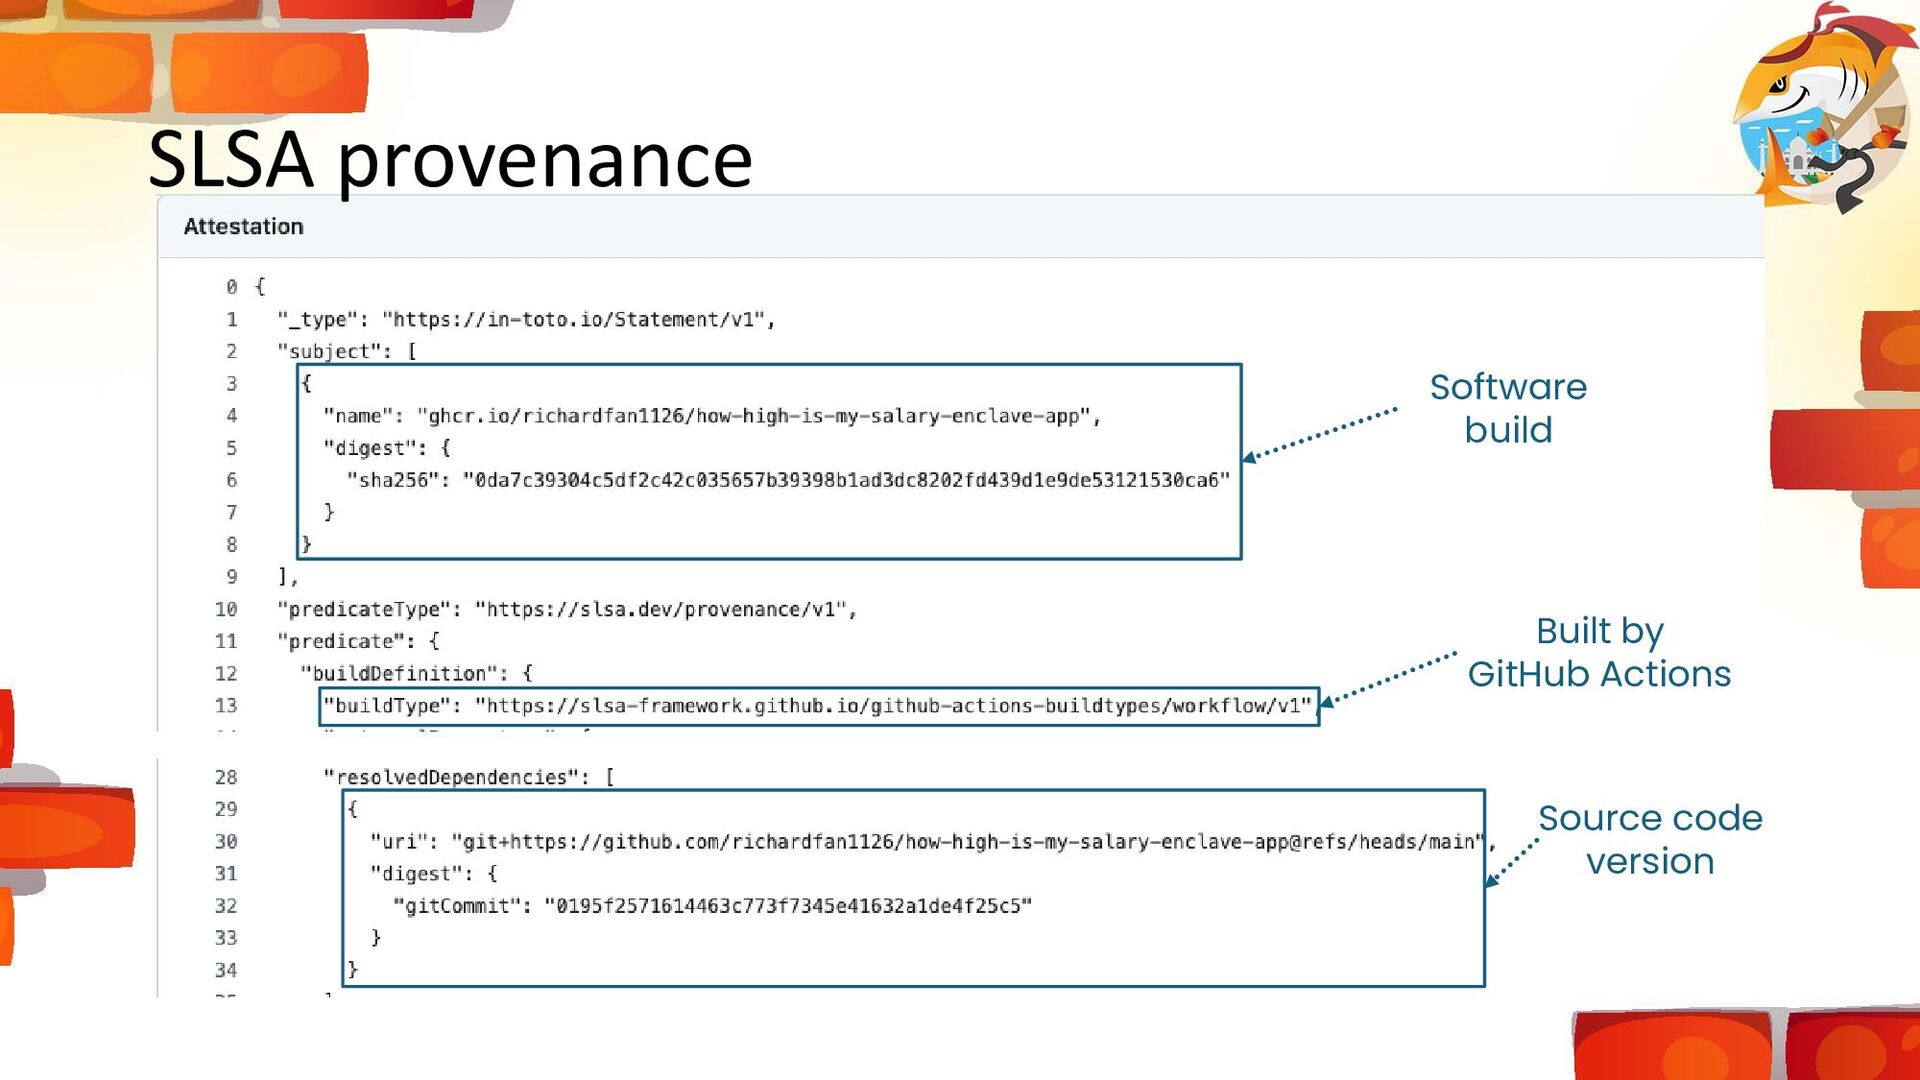
SLSA Provenance Birth certificate of the software Software
Achieving SLSA on GitHub Actions
What is GitHub Actions • CI/CD platform • Workflow defined
within code repo • Run on GitHub- / self-hosted runner
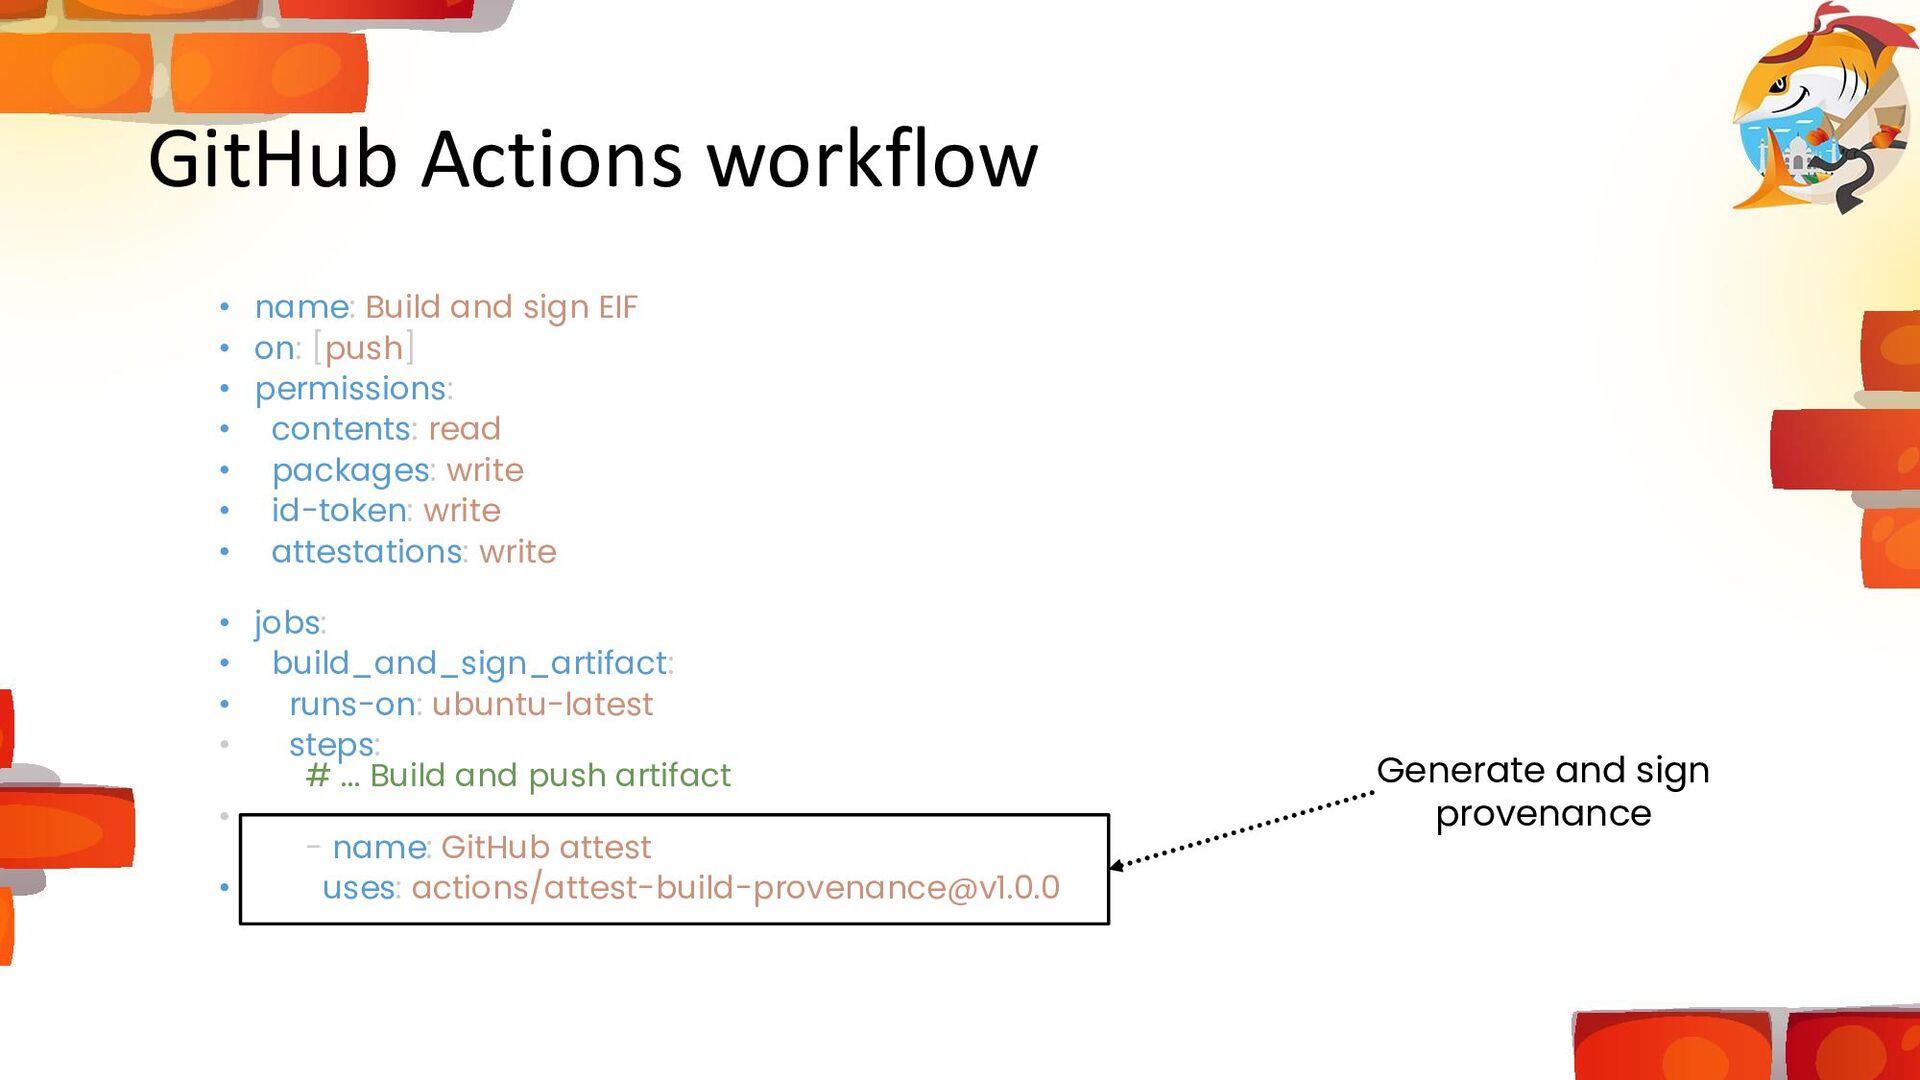
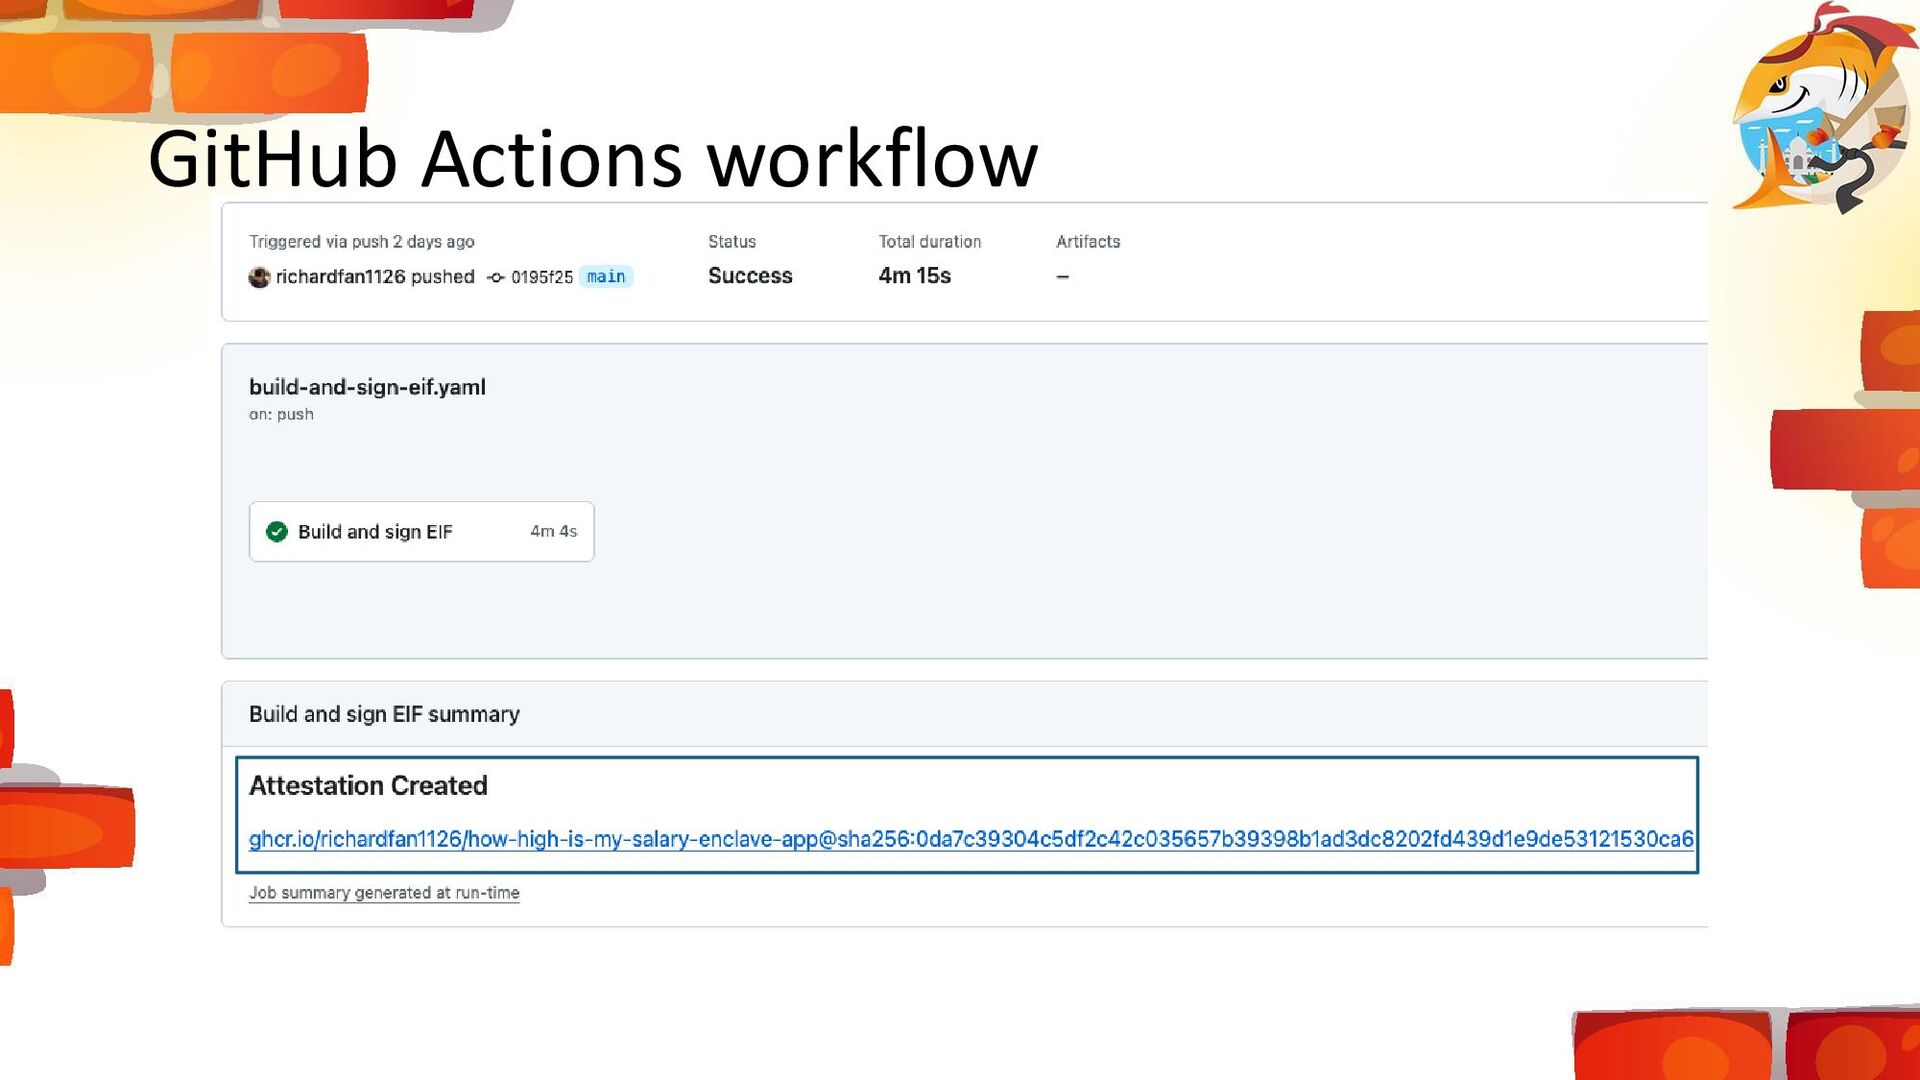
GitHub Actions workflow • name: Build and sign EIF •
on: [push] • permissions: • contents: read • packages: write • id-token: write • attestations: write • jobs: • build_and_sign_artifact: • runs-on: ubuntu-latest • steps: # ... Build and push artifact • - name: GitHub attest • uses: actions/
[email protected]
Generate and sign provenance
GitHub Actions workflow
SLSA provenance Built by GitHub Actions Source code version Software
build
Where does the software come from? Source Developers Build Package
Consumers Dependencies SLSA
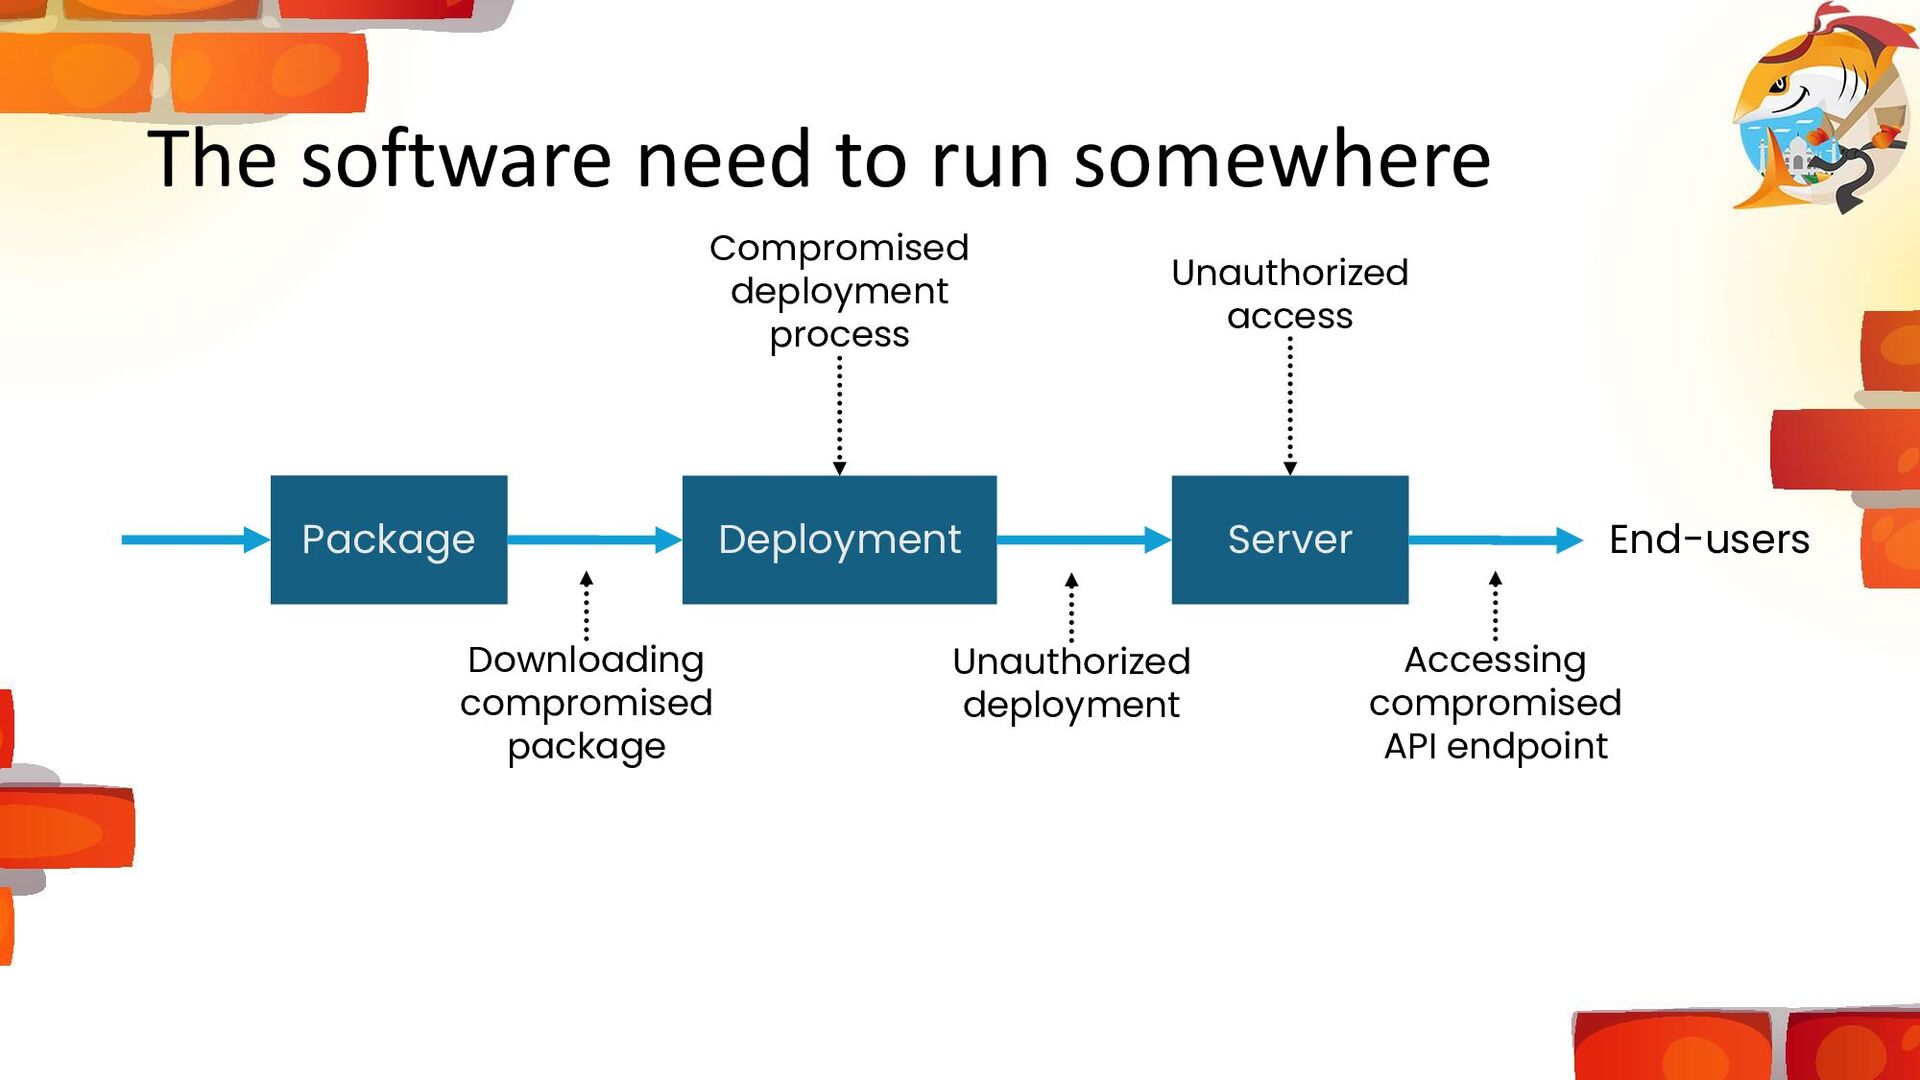
The software need to run somewhere Package Server End-users Deployment
Downloading compromised package Compromised deployment process Unauthorized deployment Unauthorized access Accessing compromised API endpoint
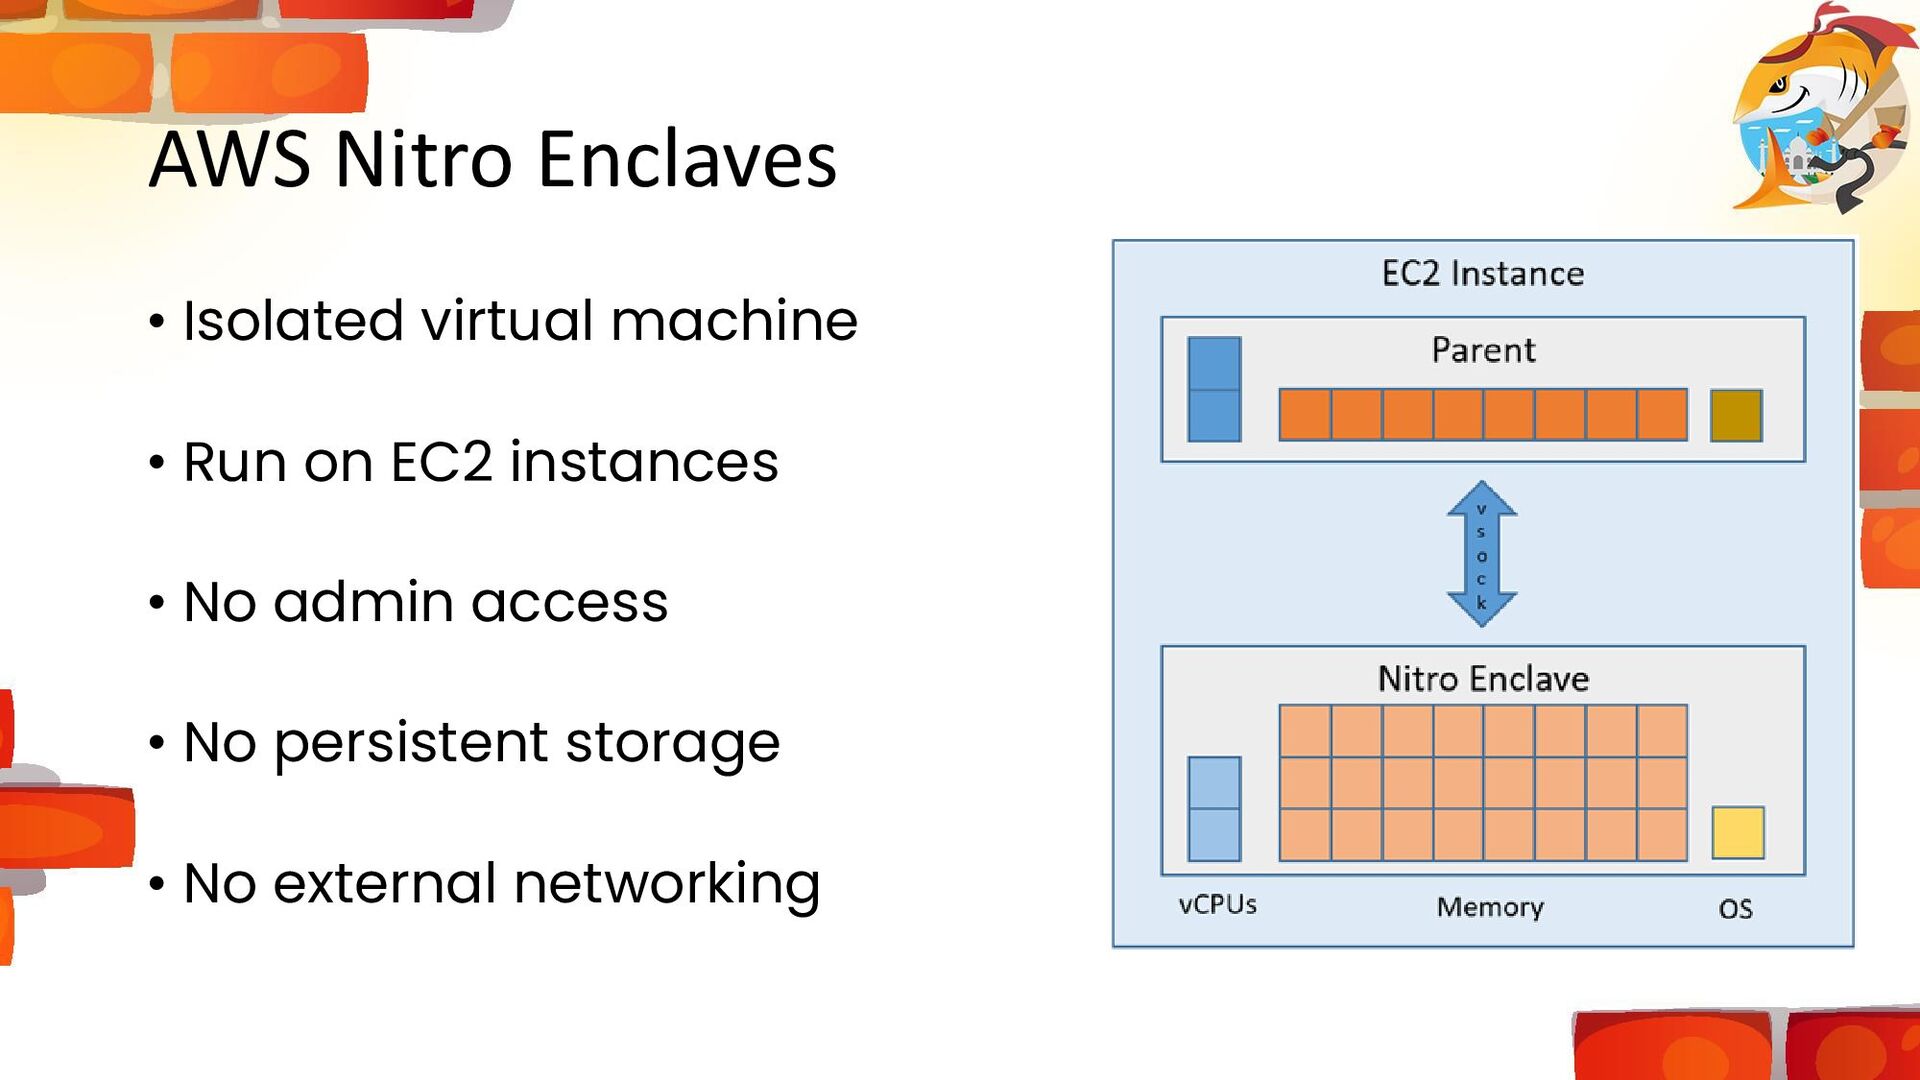
AWS Nitro Enclaves • Isolated virtual machine • Run on
EC2 instances • No admin access • No persistent storage • No external networking
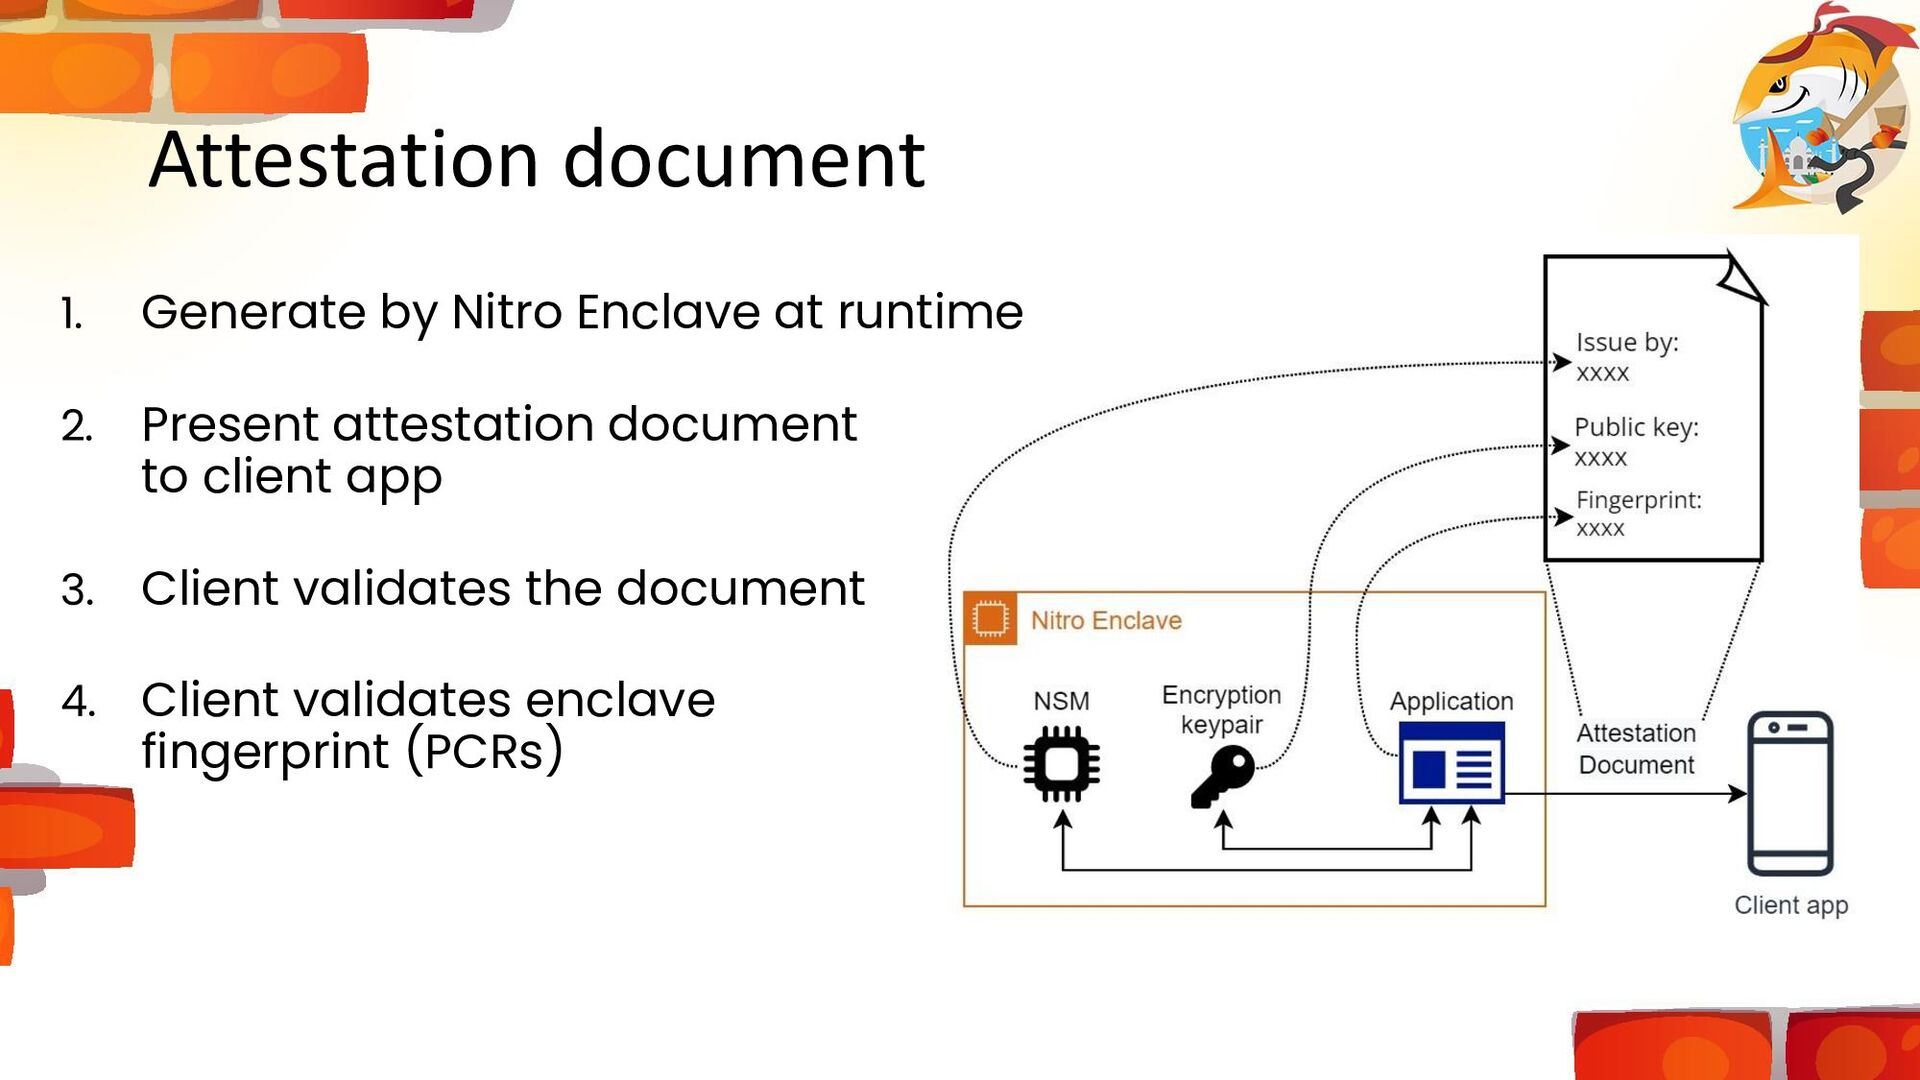
Attestation document 1. Generate by Nitro Enclave at runtime 2.
Present attestation document to client app 3. Client validates the document 4. Client validates enclave fingerprint (PCRs)
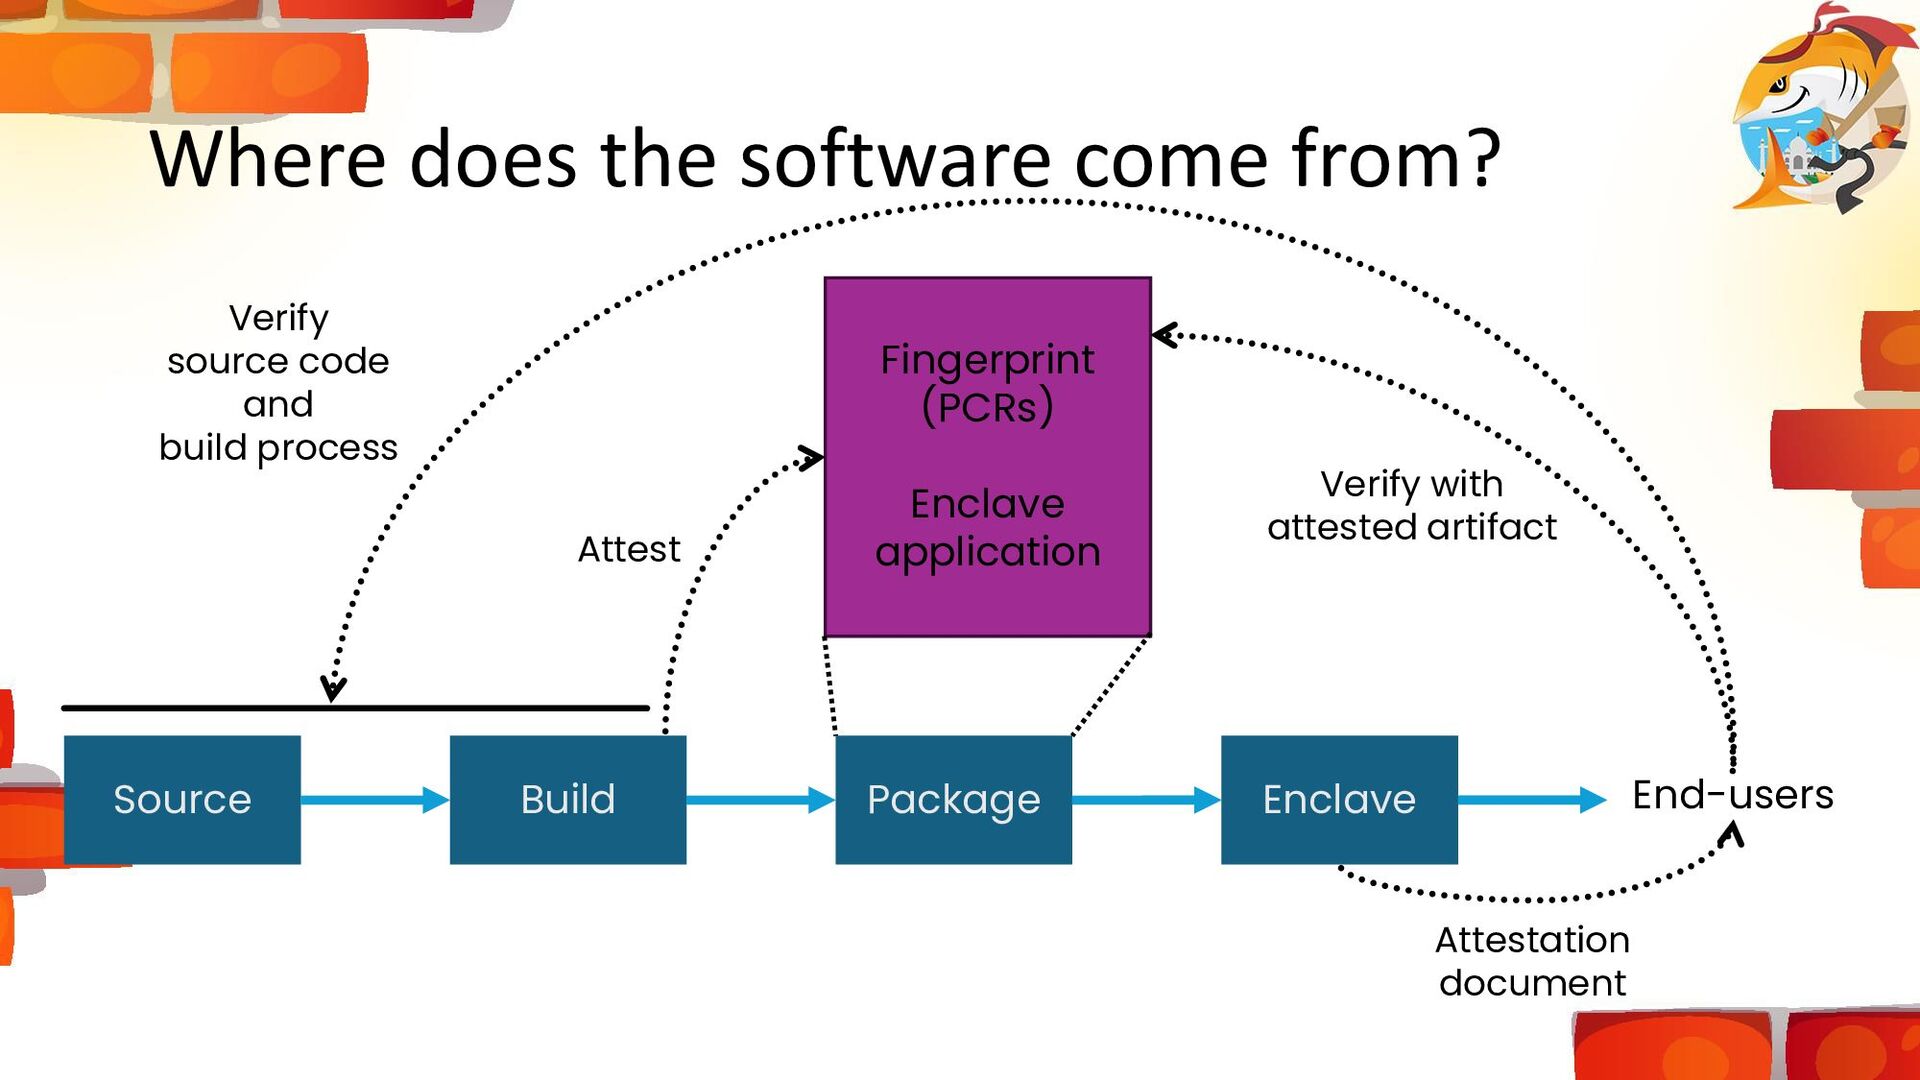
Where does the software come from? Source Build Package Fingerprint
(PCRs) Enclave application Attest Enclave End-users Attestation document Verify with attested artifact Verify source code and build process
Demo … by yourself
Demo - How high (or low) is my salary? •
This is a difficult question • I want to know how much you earn • But I don’t want you to know how much I earn
Demo - How high is my salary enclave app •
Only tell you where is your salary ranked • Source code is open • Build process is open • Run on AWS Nitro Enclave • Proved by attestation document • Data encrypted between you and the enclave
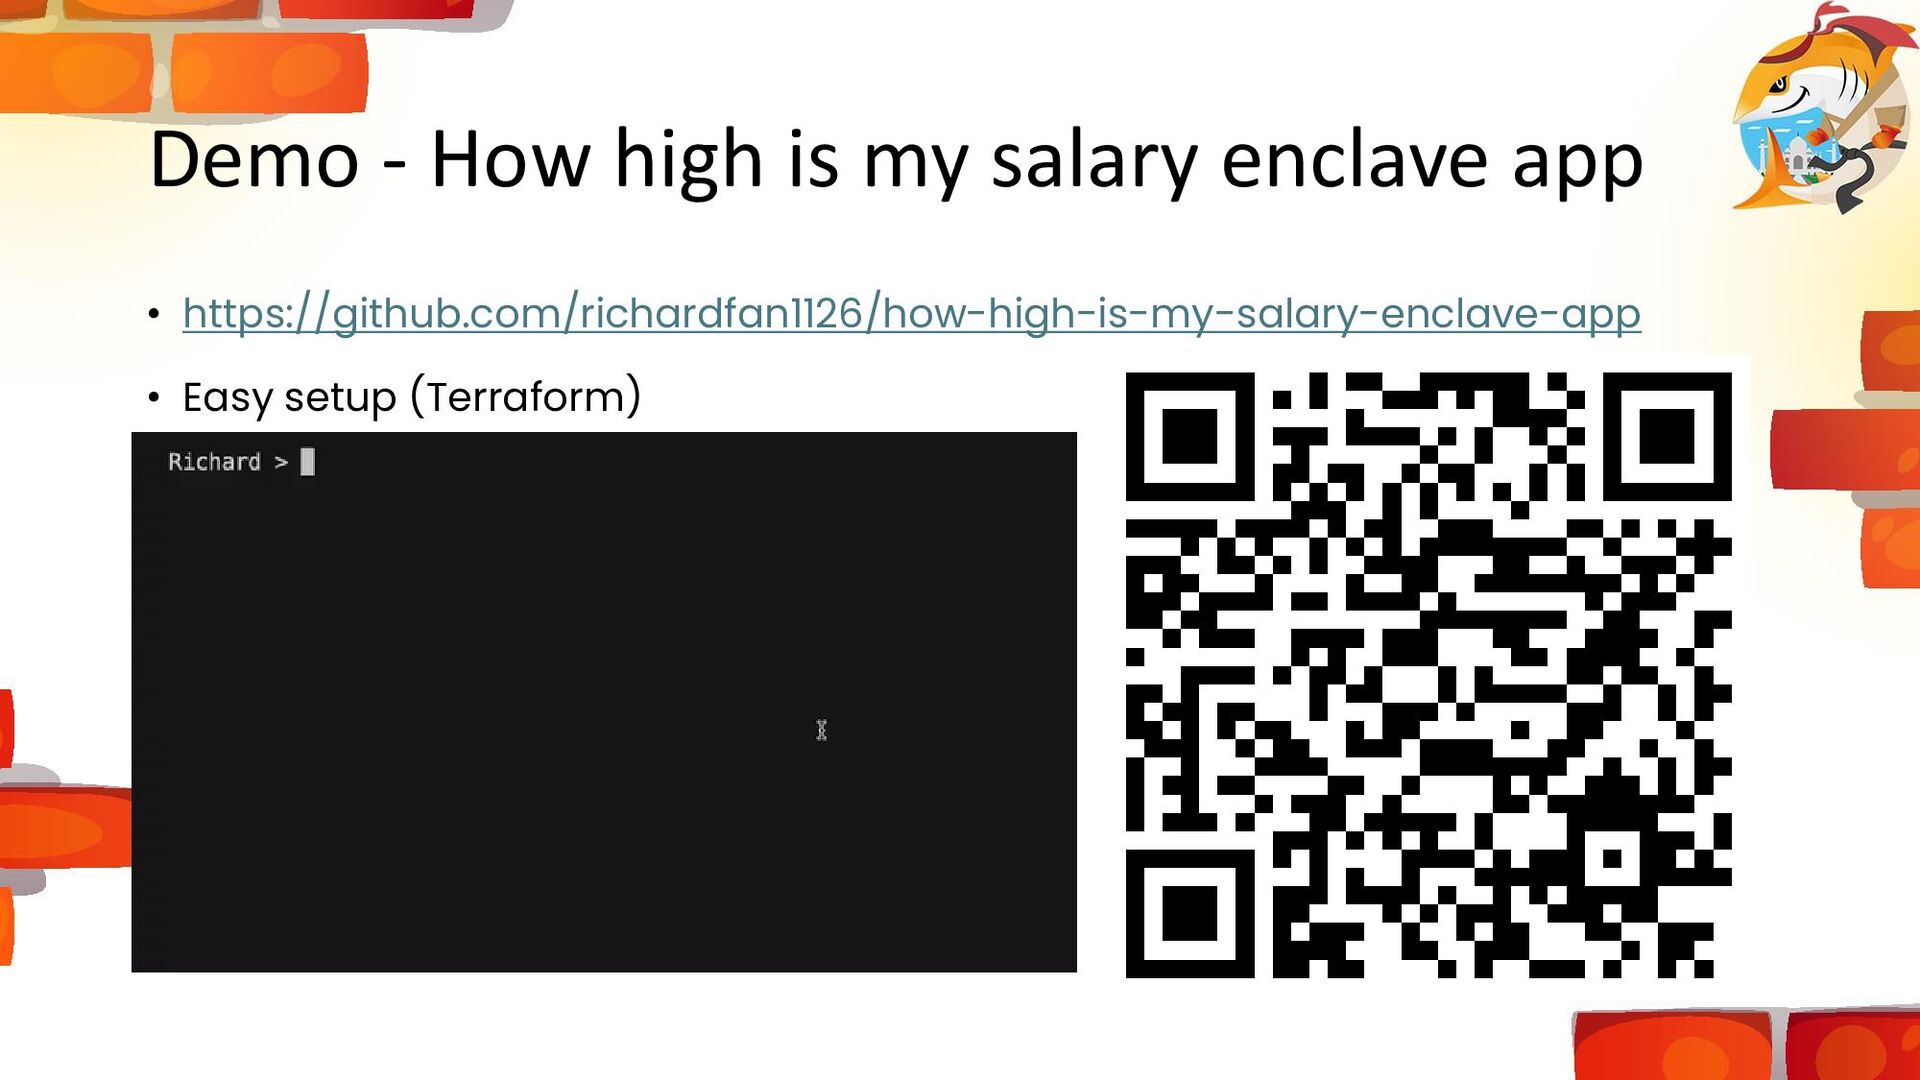
Demo - How high is my salary enclave app •
https://github.com/richardfan1126/how-high-is-my-salary-enclave-app • Easy setup (Terraform)
How to find me Richard Fan
[email protected]
20 richardfan1126


 richardfan1126
 satokan
 katzueno
 matsunobu
 tomtanaka
 nasa9084
 harappa80
 visional_engineering_and_design
 htkym
 nakanao
 masahirokawahara
 cygames
 oracle4engineer
 shpigford
 orderedlist
 caitiem20
 skipperchong
 malarkey
 csswizardry
 codingconduct
 aleyda
 matthewcrist
 rkendrick25
 mkilby
 cassininazir