Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Keeping it Clean: Sanitizing, Validating, and E...
Search
Robin Cornett
May 03, 2016
Technology
130
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Keeping it Clean: Sanitizing, Validating, and Escaping in WordPress
Robin Cornett
May 03, 2016
More Decks by Robin Cornett
See All by Robin Cornett
Accessibility Matters to You, Too
robincornett
0
440
Do You Even Need a Page Builder Anymore?
robincornett
0
40
Choosing and Managing WordPress Plugins
robincornett
0
200
The Genesis Framework Meets the Block Editor
robincornett
0
65
Mailchimp and Your Blog
robincornett
0
220
An Introduction to Chrome Dev Tools
robincornett
0
350
Front Pages and Home Pages and Posts Pages, Oh My!
robincornett
0
120
Extending WordPress with Custom Content Types
robincornett
0
270
What's New in WordPress 4.6
robincornett
0
48
Other Decks in Technology
See All in Technology
攻撃 3 時間 vs 復旧 10 時間。アクセスキー流出の非対称性を体感するために CTF を作った話
kazzpapa3
1
140
データマネジメント × 法務で作りあげる、 freeeの新しいデータガバナンスへの軌跡
freee
PRO
3
690
OneLakeをデータソースにした AI Search(Foundry IQ)の ライフサイクル管理
ryuseiiida
0
220
FinOpsを導入してマルチプロダクトのコスト最適化を実現する
kworkdev
PRO
0
120
SLOを阻む不安
sraku2159
0
210
AI時代の開発はウォーターフォールに回帰する? / development-with-ai-back-to-wf
okamototakuyasr2
0
170
ドメインエキスパートは いかにして AI を使って プロダクト開発をするか
tatsuyashiraishi
1
260
AIがGISを代替する日:〜すべてをAIが創る時代に、私たちがFOSS4Gに関わる意味〜
lehupa
0
200
eBPF 簡介 2026 版
shunghsiyu
0
160
Lint の層を組み直した話
bengo4com
2
300
現場を動かすAIエージェント#2_製造業現場でのAI活用から見た、ハマる罠と実践知
kintotechdev
1
120
(swiftc) NonCopyableとライフタイム修飾子
teamhimeh
0
170
Featured
See All Featured
Chasing Engaging Ingredients in Design
codingconduct
0
380
How to Grow Your eCommerce with AI & Automation
katarinadahlin
PRO
2
340
Mobile First: as difficult as doing things right
swwweet
225
10k
Fantastic passwords and where to find them - at NoRuKo
philnash
53
4k
How to build an LLM SEO readiness audit: a practical framework
nmsamuel
2
970
Paper Plane (Part 1)
katiecoart
PRO
2
12k
世界の人気アプリ100個を分析して見えたペイウォール設計の心得
akihiro_kokubo
PRO
74
43k
HU Berlin: Industrial-Strength Natural Language Processing with spaCy and Prodigy
inesmontani
PRO
0
790
Leveraging LLMs for student feedback in introductory data science courses - posit::conf(2025)
minecr
1
460
The Power of CSS Pseudo Elements
geoffreycrofte
82
6.6k
Fireside Chat
paigeccino
43
4.1k
Learning to Love Humans: Emotional Interface Design
aarron
275
41k
Transcript
KEEPING IT CLEAN Sanitizing, Validating, and Escaping in WordPress
ASSUME THAT EVERYONE AROUND YOU IS LYING (or clueless, confused,
lost, can’t/won’t read, crazy)
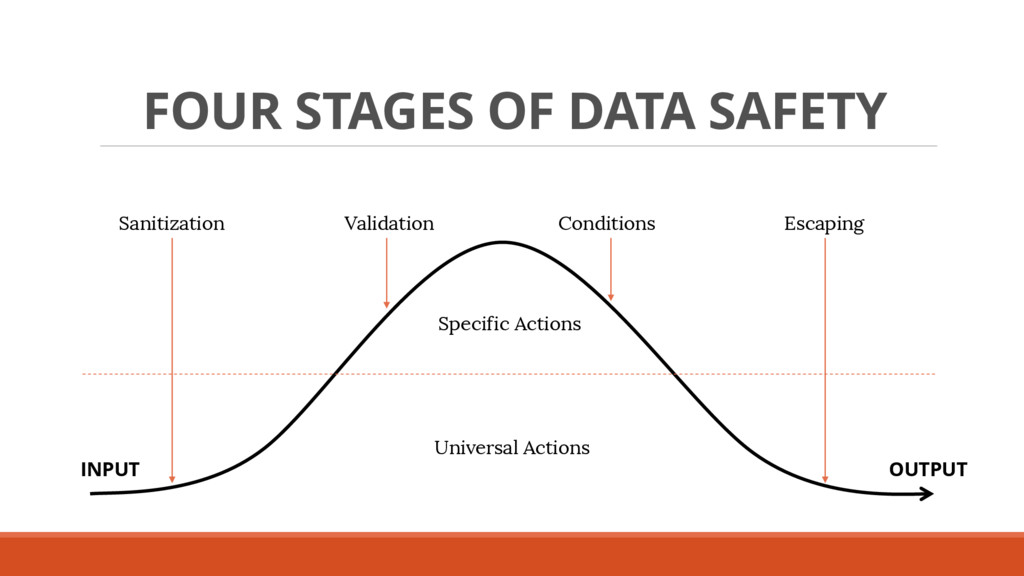
FOUR STAGES OF DATA SAFETY Sanitization Validation Conditions Escaping Universal
Actions Specific Actions INPUT OUTPUT
INPUT: SANITIZE FOR SANITY Save the Right Kind of Data
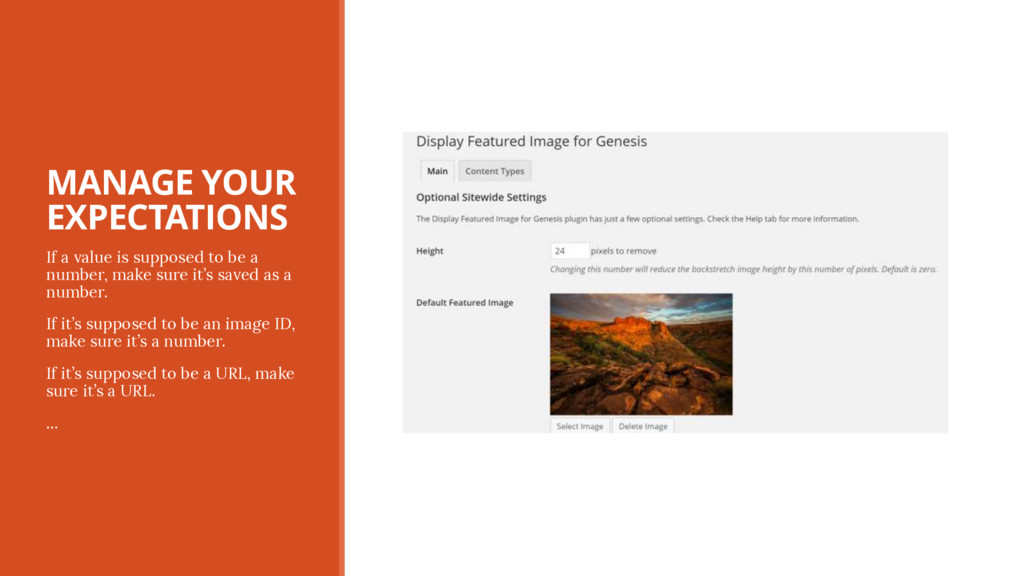
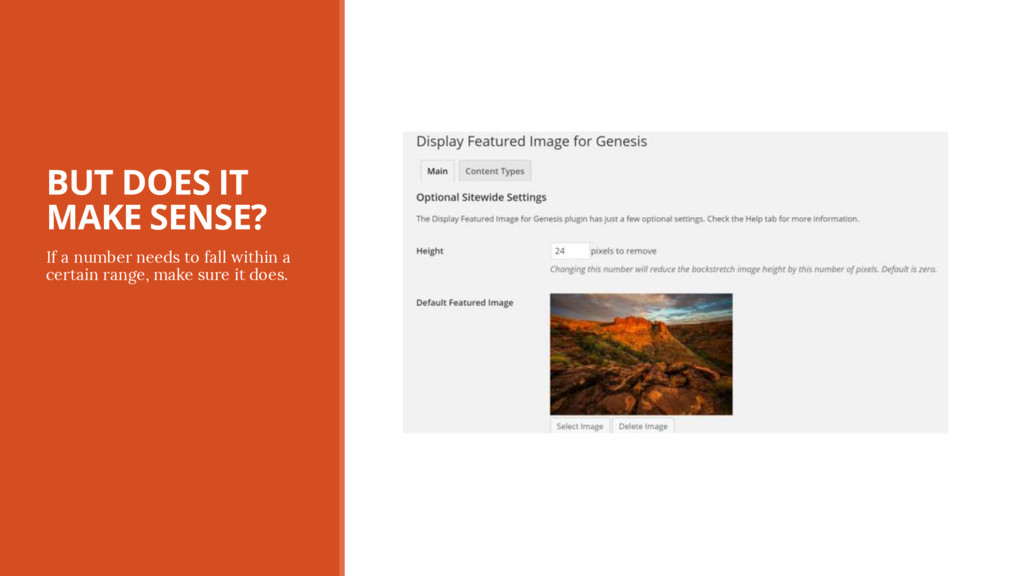
DISPLAY FEATURED IMAGE FOR GENESIS
MANAGE YOUR EXPECTATIONS If a value is supposed to be
a number, make sure it’s saved as a number. If it’s supposed to be an image ID, make sure it’s a number. If it’s supposed to be a URL, make sure it’s a URL. …
BE RUTHLESS When you have a range of data that
can be entered, make sure you sanitize it.
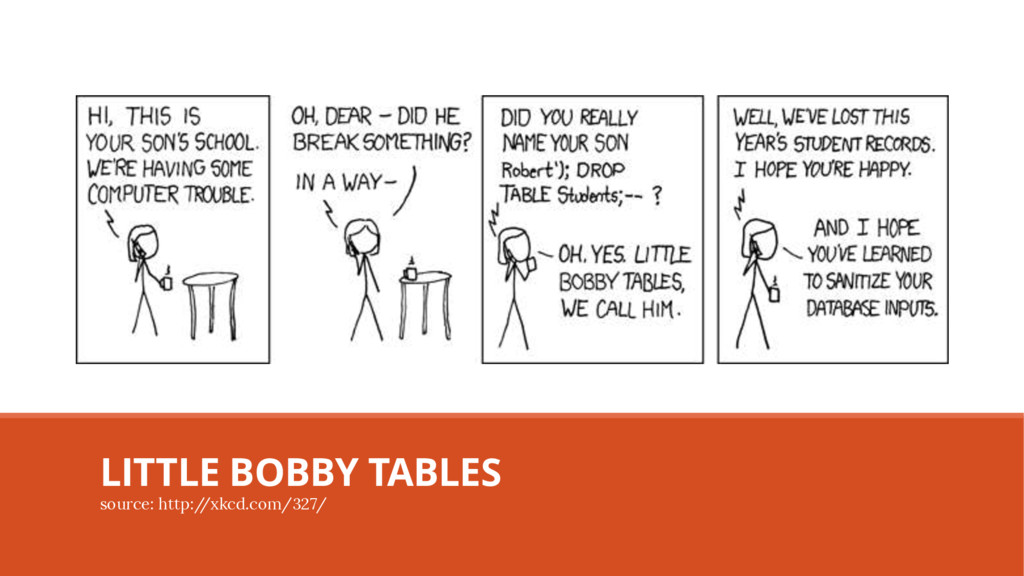
LITTLE BOBBY TABLES source: http:/ /xkcd.com/327/
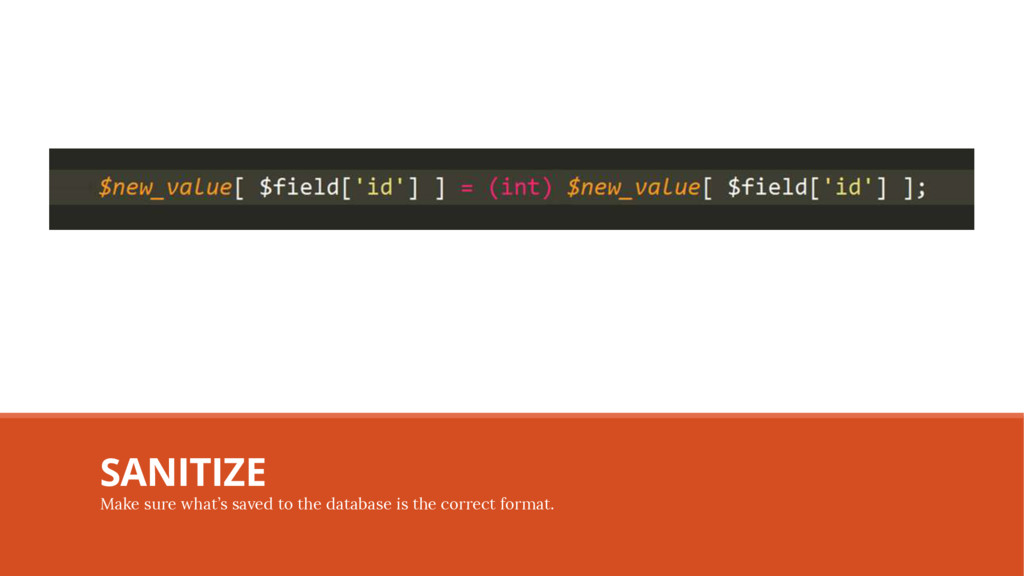
SANITIZE Make sure what’s saved to the database is the
correct format.
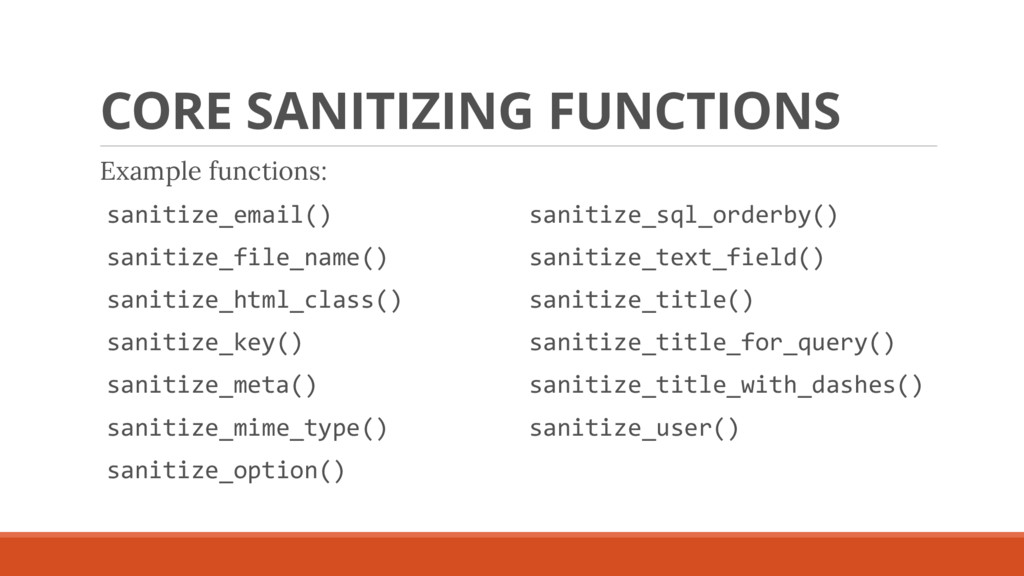
CORE SANITIZING FUNCTIONS Example functions: sanitize_email() sanitize_file_name() sanitize_html_class() sanitize_key() sanitize_meta()
sanitize_mime_type() sanitize_option() sanitize_sql_orderby() sanitize_text_field() sanitize_title() sanitize_title_for_query() sanitize_title_with_dashes() sanitize_user()
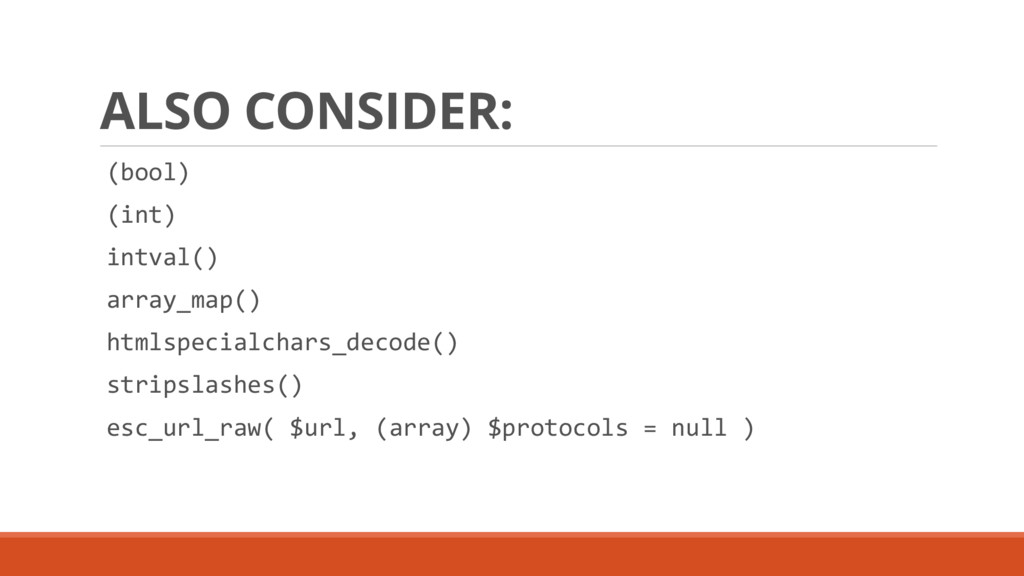
ALSO CONSIDER: (bool) (int) intval() array_map() htmlspecialchars_decode() stripslashes() esc_url_raw( $url,
(array) $protocols = null )
INPUT: VALIDATE FOR LOGIC Make Sure the Data Makes Sense
BE RUTHLESS Follow the whitelist philosophy with data validation, and
only allow the user to input data of your expected type. If it's not the proper type, discard it.
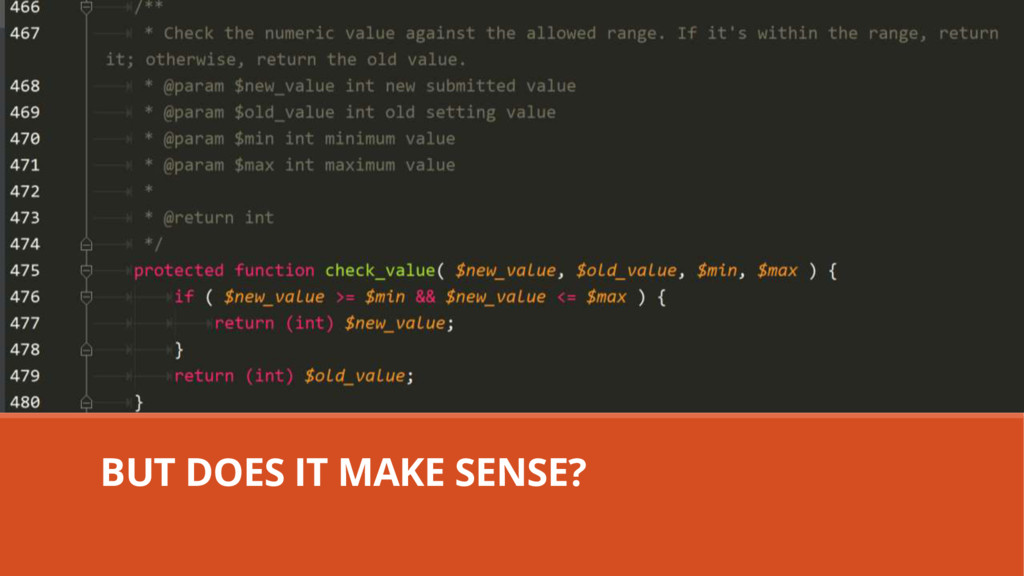
BUT DOES IT MAKE SENSE? If a number needs to
fall within a certain range, make sure it does.
BUT DOES IT MAKE SENSE?
OUTPUT: IT DEPENDS Use Conditionals To Make Smart Decisions
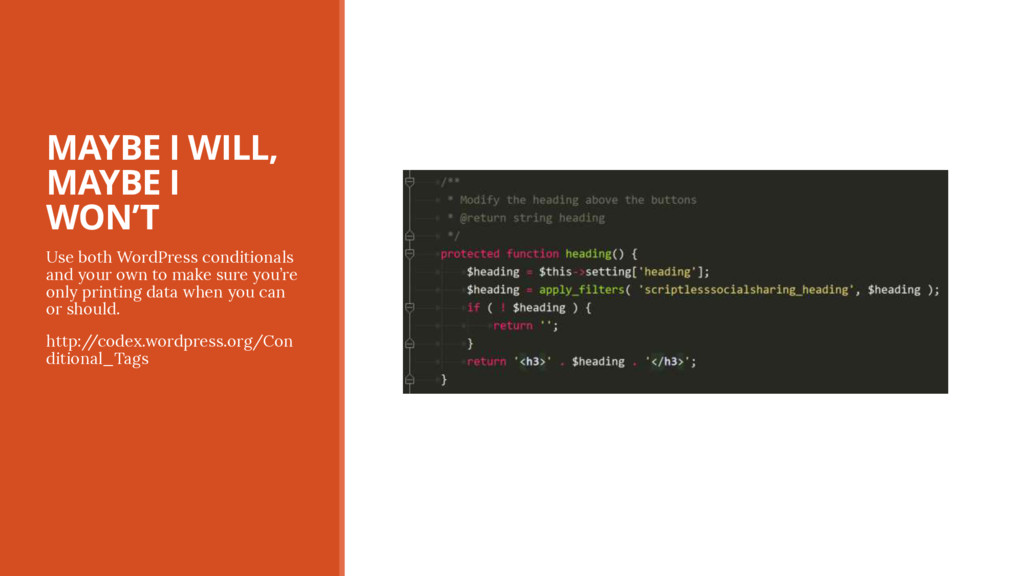
MAYBE I WILL, MAYBE I WON’T Use both WordPress conditionals
and your own to make sure you’re only printing data when you can or should. http:/ /codex.wordpress.org/Con ditional_Tags
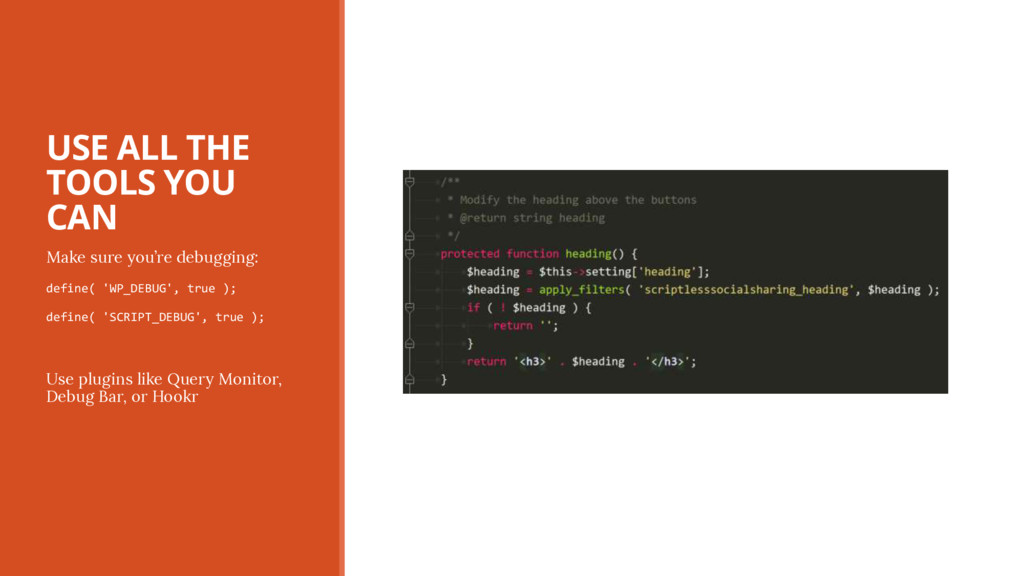
USE ALL THE TOOLS YOU CAN Make sure you’re debugging:
define( 'WP_DEBUG', true ); define( 'SCRIPT_DEBUG', true ); Use plugins like Query Monitor, Debug Bar, or Hookr
OUTPUT: ESCAPE ALL THE THINGS
None
ESCAPE ALL THE THINGS “Escaping changes possibly evil content into
safe content.” source: https:/ /css-tricks.com/introduction-to-wordpress-front-end-security-escaping-the-things/
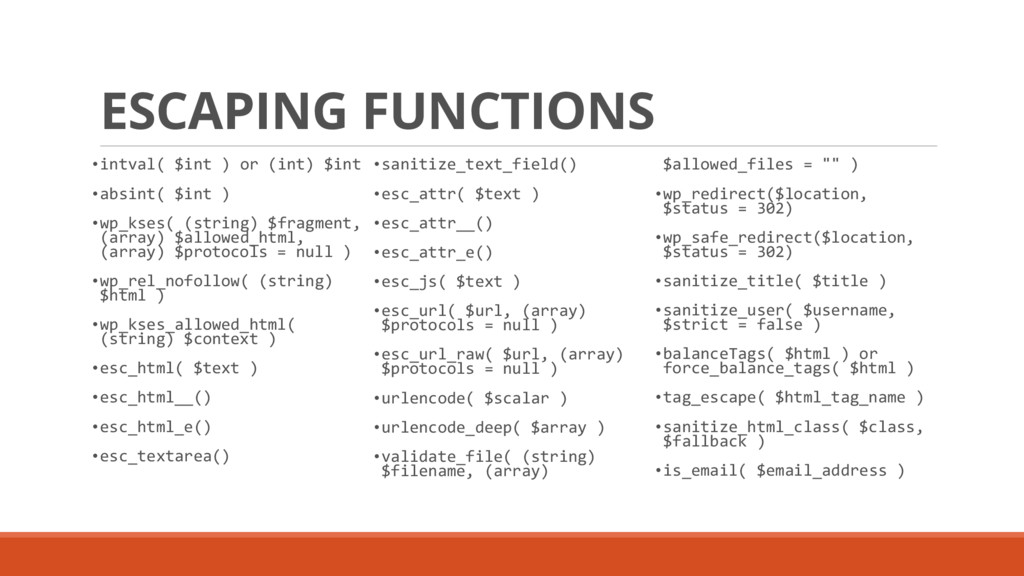
ESCAPING FUNCTIONS •intval( $int ) or (int) $int •absint( $int
) •wp_kses( (string) $fragment, (array) $allowed_html, (array) $protocols = null ) •wp_rel_nofollow( (string) $html ) •wp_kses_allowed_html( (string) $context ) •esc_html( $text ) •esc_html__() •esc_html_e() •esc_textarea() •sanitize_text_field() •esc_attr( $text ) •esc_attr__() •esc_attr_e() •esc_js( $text ) •esc_url( $url, (array) $protocols = null ) •esc_url_raw( $url, (array) $protocols = null ) •urlencode( $scalar ) •urlencode_deep( $array ) •validate_file( (string) $filename, (array) $allowed_files = "" ) •wp_redirect($location, $status = 302) •wp_safe_redirect($location, $status = 302) •sanitize_title( $title ) •sanitize_user( $username, $strict = false ) •balanceTags( $html ) or force_balance_tags( $html ) •tag_escape( $html_tag_name ) •sanitize_html_class( $class, $fallback ) •is_email( $email_address )
BE RUTHLESS Escape data as much as possible on output
to avoid XSS and malformed HTML.
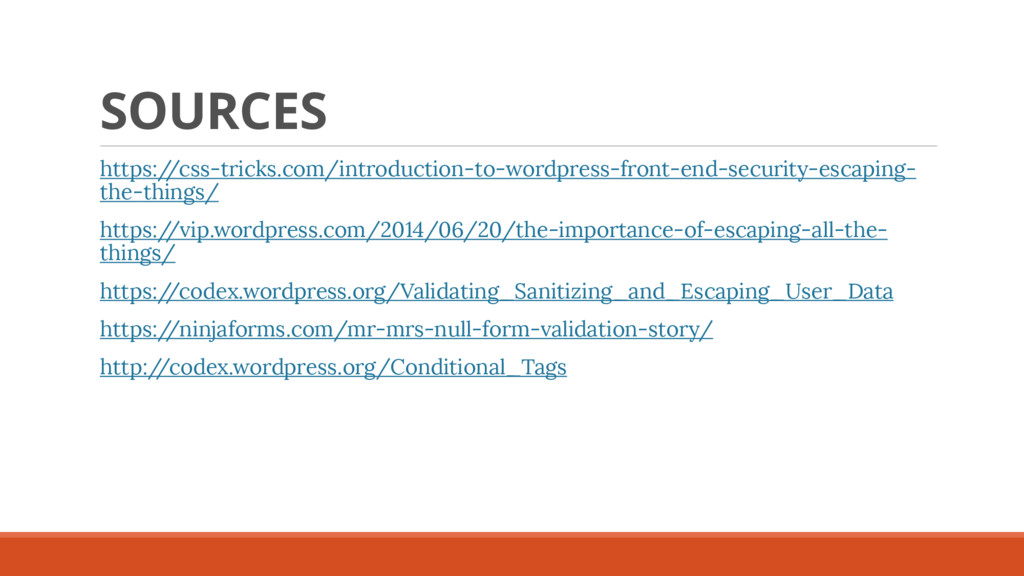
SOURCES https:/ /css-tricks.com/introduction-to-wordpress-front-end-security-escaping- the-things/ https:/ /vip.wordpress.com/2014/06/20/the-importance-of-escaping-all-the- things/ https:/ /codex.wordpress.org/Validating_Sanitizing_and_Escaping_User_Data https:/
/ninjaforms.com/mr-mrs-null-form-validation-story/ http:/ /codex.wordpress.org/Conditional_Tags
THANK YOU robincornett.com @robincornett


 robincornett
 kazzpapa3
 freee
 ryuseiiida
 kworkdev
 sraku2159
 okamototakuyasr2
 tatsuyashiraishi
 lehupa
 shunghsiyu
 bengo4com
 kintotechdev
 teamhimeh
 codingconduct
 katarinadahlin
 swwweet
 philnash
 nmsamuel
 katiecoart
 akihiro_kokubo
 inesmontani
 minecr
 geoffreycrofte
 paigeccino
 aarron