Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
OAuth 2 und OpenID Connect @DevSec 2017
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Simon Kölsch
October 26, 2017
Education
86
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
OAuth 2 und OpenID Connect @DevSec 2017
//heise devSec() 26, oct, 2017
Simon Kölsch
October 26, 2017
More Decks by Simon Kölsch
See All by Simon Kölsch
Vault @ Continuous Lifecycle 2016
simkoelsch
0
210
Security in Microservices Umgebungen @WJAX2016
simkoelsch
0
79
Secure Clojure Webapplications @ Froscon
simkoelsch
0
140
Docker Introduction Tech Talk
simkoelsch
0
150
Web Crypto API - Talk @EnterJS
simkoelsch
1
170
OAuth 2 und OpenID Connect @JAX2015
simkoelsch
2
490
Web Crypto API - Lightning Talk @Troopers
simkoelsch
1
130
Other Decks in Education
See All in Education
DRONEGEOGRAFÍA: INNOVACIÓN DIDÁCTICA Y FOTOGRAMETRÍA 3D PARA LA COHESIÓN TERRITORIAL Y LA CIUDADANÍA ACTIVA
juanmartin2026
0
39k
AIでアウトプットできる時代だからこそ、自分の言葉で考えることの大切さ / What's Left to Think, When AI Can Write?
masakiokuda
1
360
Book-keeping
bvr7352
0
130
El Clima de España. Tema 2 (PPT)
juanmartin2026
0
19k
学生のうちに考えておきたい信頼の話
suisan
1
840
ちいかわを読め
uchi8977
1
410
[2026後期火5] 論理学(京都大学文学部 後期 第2回)「量化子の導入」
yatabe
0
180
Adobe Express
matleenalaakso
2
8.4k
EL GEOPARQUE MUNDIAL UNESCO VOLCANES DE CALATRAVA: DE LA INVESTIGACIÓN CIENTÍFICA A LA TRANSPOSICIÓN DIDÁCTICA EN EL AULA
juanmartin2026
0
32k
Introduction - Lecture 1 - Human-Computer Interaction (1023841ANR)
signer
PRO
0
3.5k
Modulo : abc
robintux
0
240
An Experiment in "Cross-Cultural Exchange" as a Method for Content Creation
naoji_taniguchi_ksk_0827
0
250
Featured
See All Featured
Designing for Timeless Needs
cassininazir
1
530
What Being in a Rock Band Can Teach Us About Real World SEO
427marketing
0
1.1k
Rails Girls Zürich Keynote
gr2m
96
14k
Side Projects
sachag
456
43k
The Hidden Cost of Media on the Web [PixelPalooza 2025]
tammyeverts
2
530
Put a Button on it: Removing Barriers to Going Fast.
kastner
60
4.6k
It's Worth the Effort
3n
188
29k
Imperfection Machines: The Place of Print at Facebook
scottboms
270
14k
So, you think you're a good person
axbom
PRO
2
2.2k
Creating an realtime collaboration tool: Agile Flush - .NET Oxford
marcduiker
35
2.6k
HDC tutorial
michielstock
2
960
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
730
Transcript
OAuth 2 und OpenID Connect //heise devSec() 2015 26.10.2017, Heidelberg
Simon Kölsch & Christoph Iserlohn
Agenda > OAuth 1, OAuth 2, OpenID Connect, O…? >
How does it work? > Use Cases > Should I use it
“Web 2.0” Platforms and many more…
“Web 2.0” Platforms and many more… = User content on
big platforms with APIs 2010 - ~ 550.000 “Facebook Apps” 2015 - ~ 30 Flickr Apps tagged “geo” …
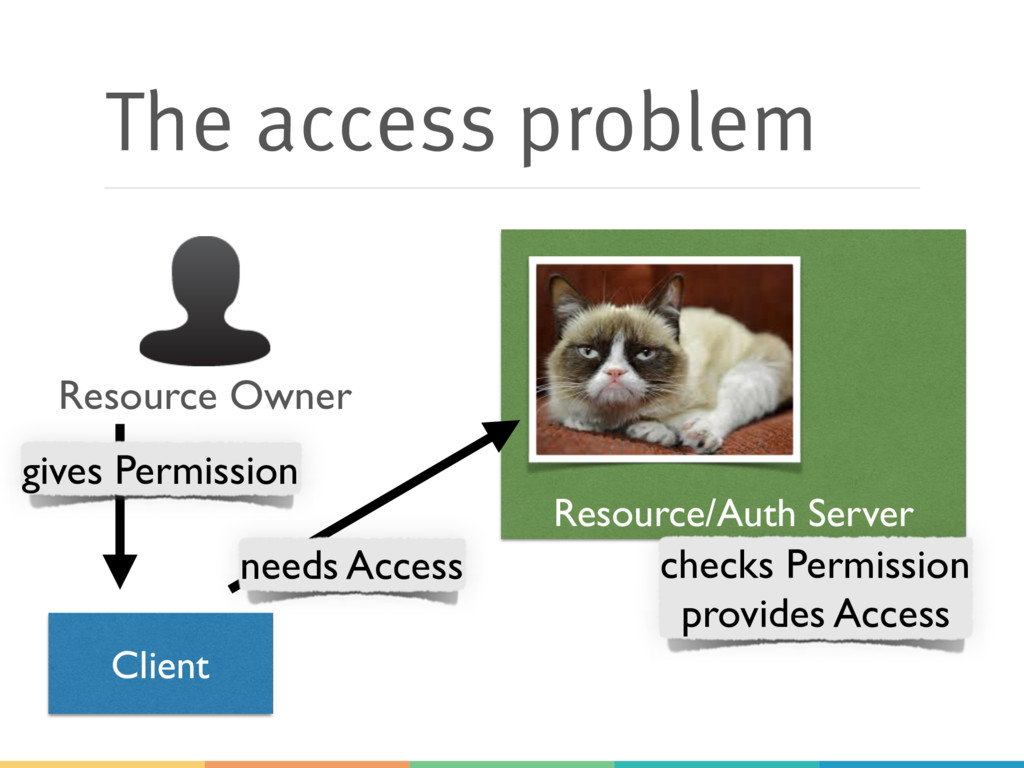
Resource/Auth Server The access problem Client Resource Owner needs Access
checks Permission provides Access gives Permission
OAuth 0 > Client gets user password > Client impersonates
user and gets resource
OAuth 1 > Client registers at the service > Client
asks resource owner for permission via the service > Client gets a token > Client can access the resource with the token
OAuth 1 > Authorization Protocol > RFC 5849 (38 pages
spec) > One security issue (fixed 2009) > non-trivial request / response creation > Scope: “web applications”
Why OAuth 2? > Simplify client development process > Desktop
Applications / Single-Page-Apps > Mobile Phones > “Living room devices”
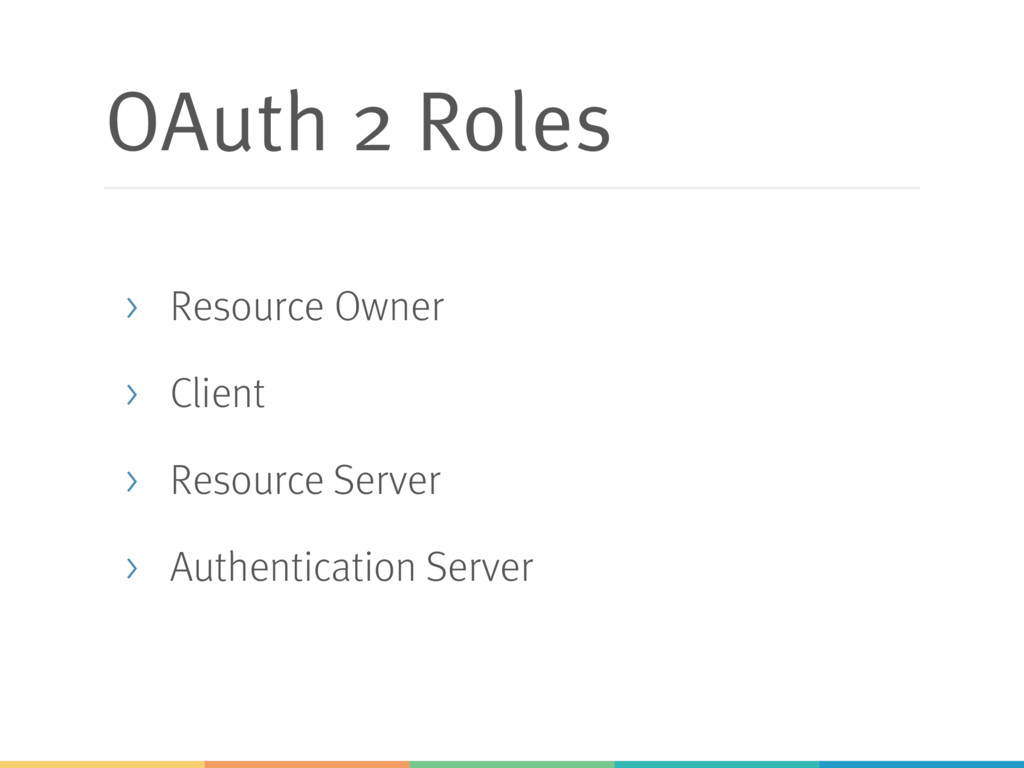
OAuth 2 Roles > Resource Owner > Client > Resource
Server > Authentication Server
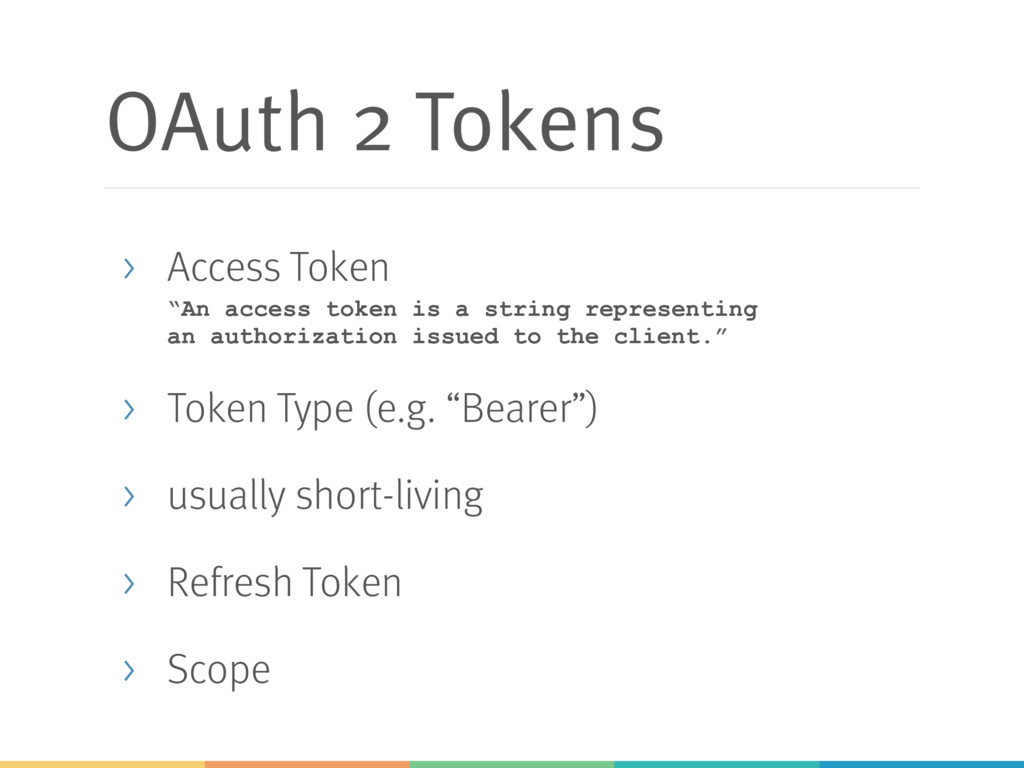
OAuth 2 Tokens > Access Token “An access token is
a string representing an authorization issued to the client.” > Token Type (e.g. “Bearer”) > usually short-living > Refresh Token > Scope
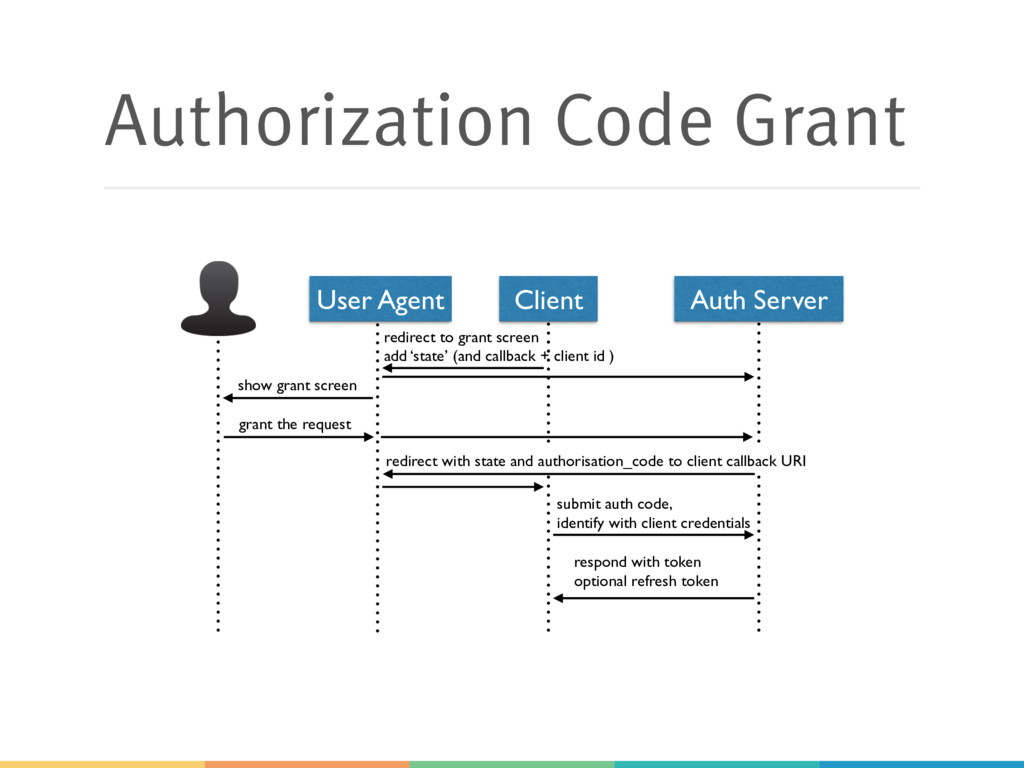
Authorization Code Grant User Agent Client Auth Server redirect to
grant screen add ‘state’ (and callback + client id ) show grant screen grant the request redirect with state and authorisation_code to client callback URI submit auth code, identify with client credentials respond with token optional refresh token
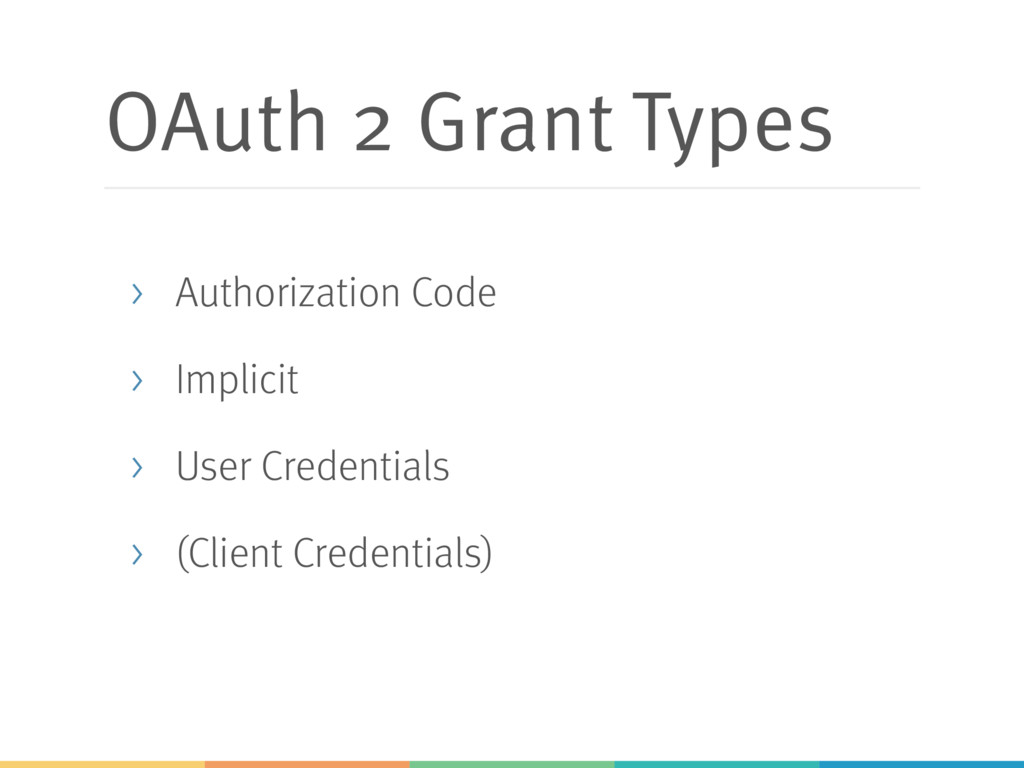
OAuth 2 Grant Types > Authorization Code > Implicit >
User Credentials > (Client Credentials)
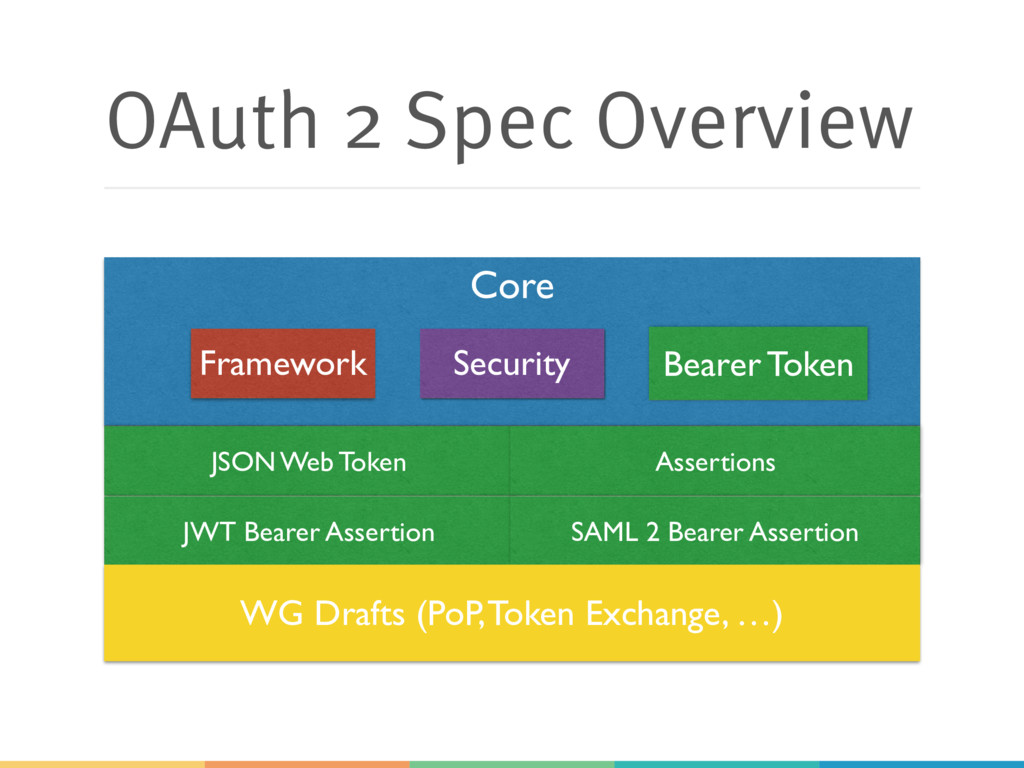
OAuth 2 Spec Overview Core Framework Bearer Token Security JSON
Web Token Assertions JWT Bearer Assertion SAML 2 Bearer Assertion WG Drafts (PoP, Token Exchange, …)
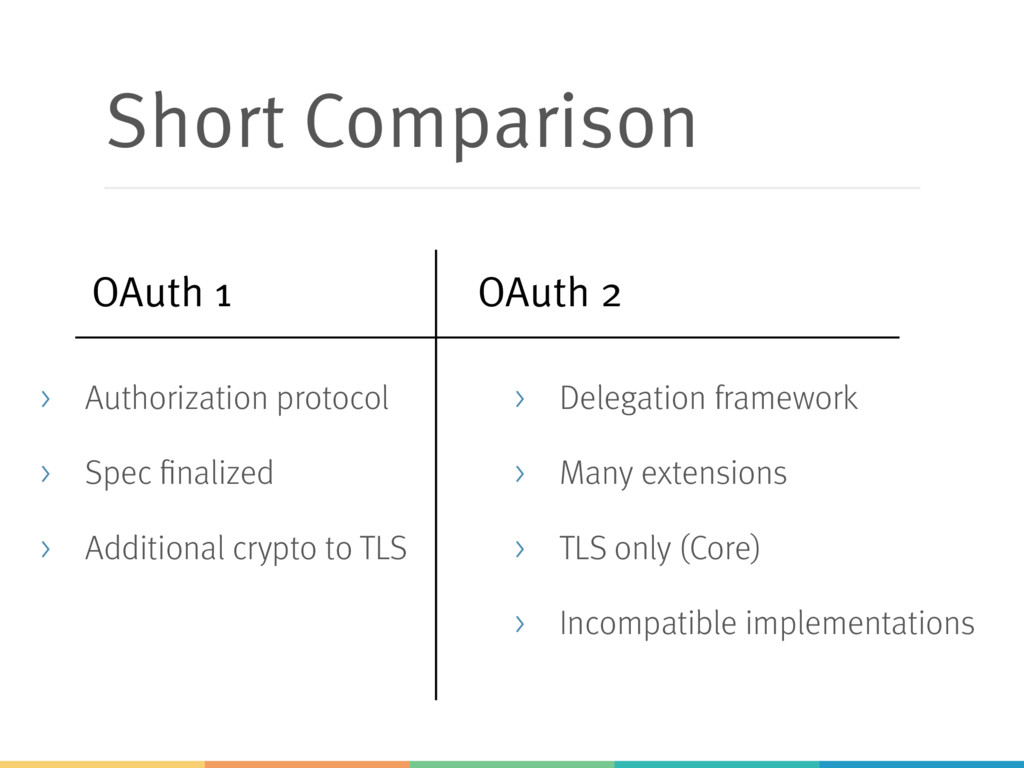
Short Comparison OAuth 1 OAuth 2 > Authorization protocol >
Spec finalized > Additional crypto to TLS > Delegation framework > Many extensions > TLS only (Core) > Incompatible implementations
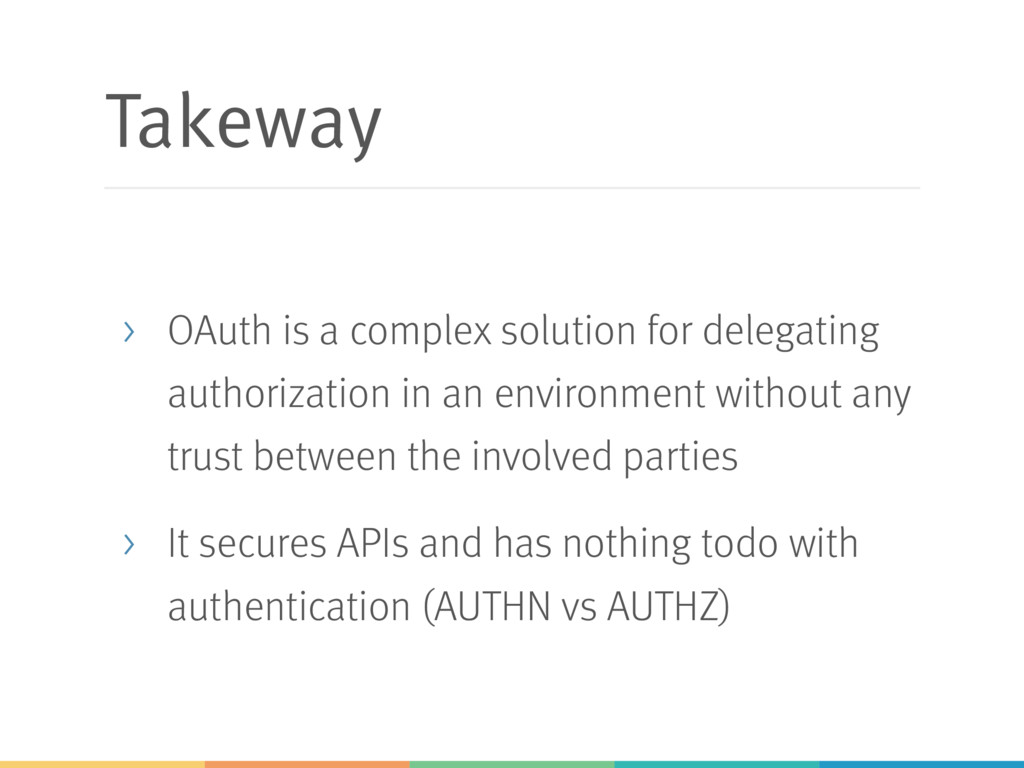
Takeway > OAuth is a complex solution for delegating authorization
in an environment without any trust between the involved parties > It secures APIs and has nothing todo with authentication (AUTHN vs AUTHZ)
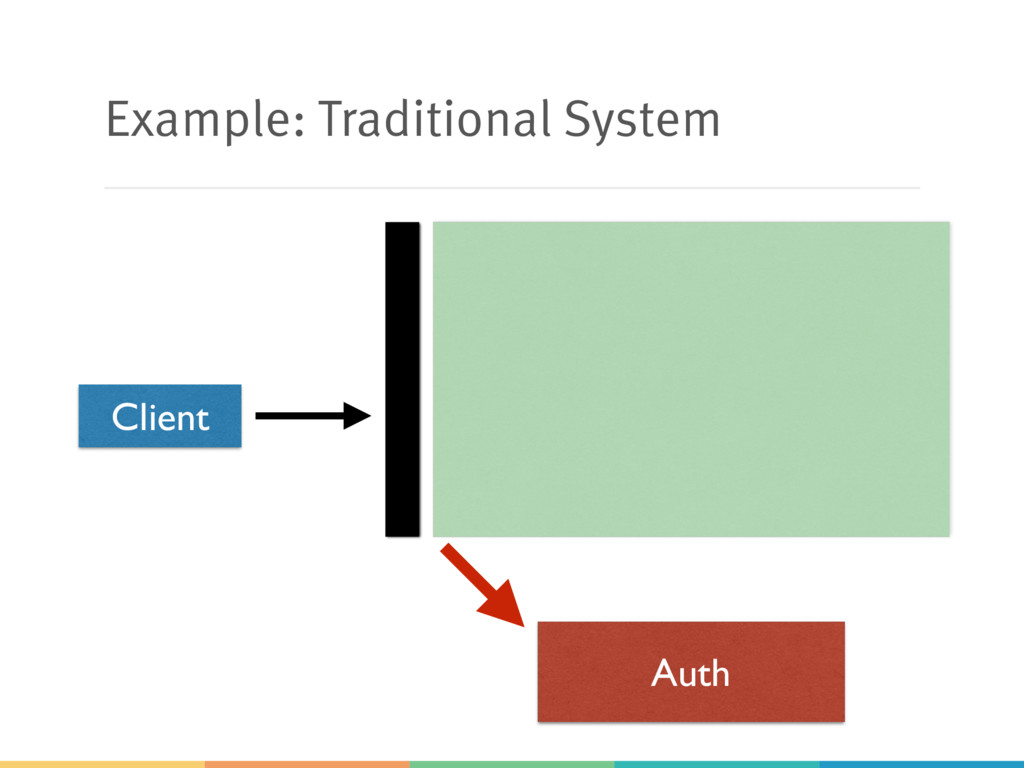
Example: Traditional System Client Auth
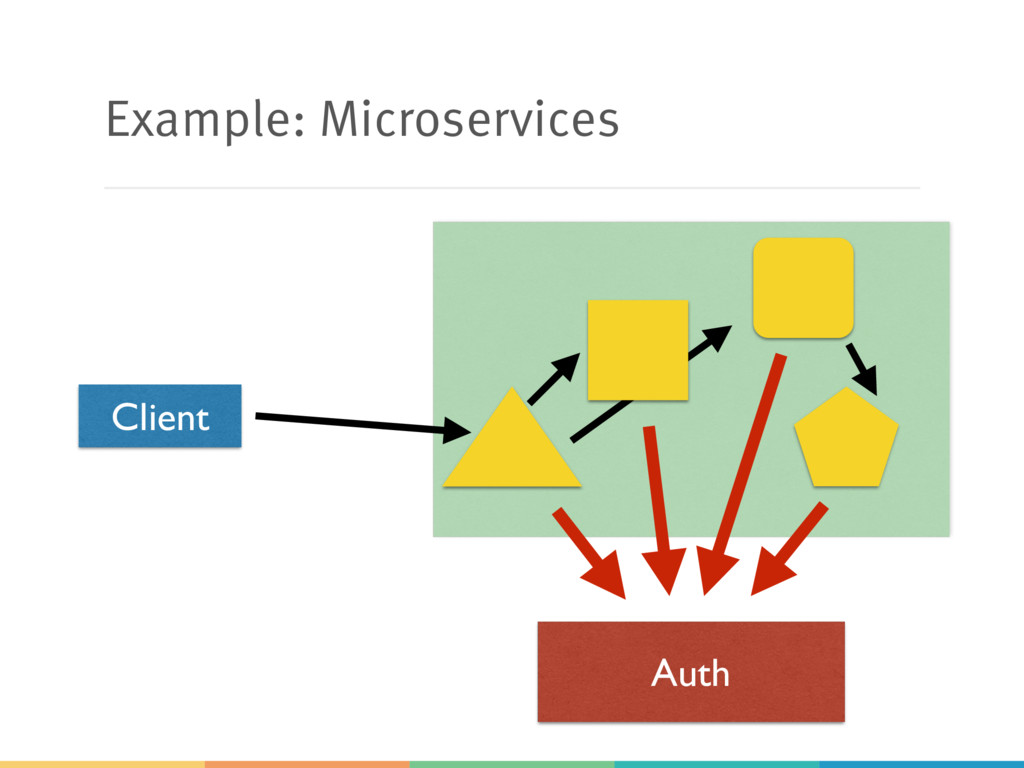
Example: Microservices Client Auth
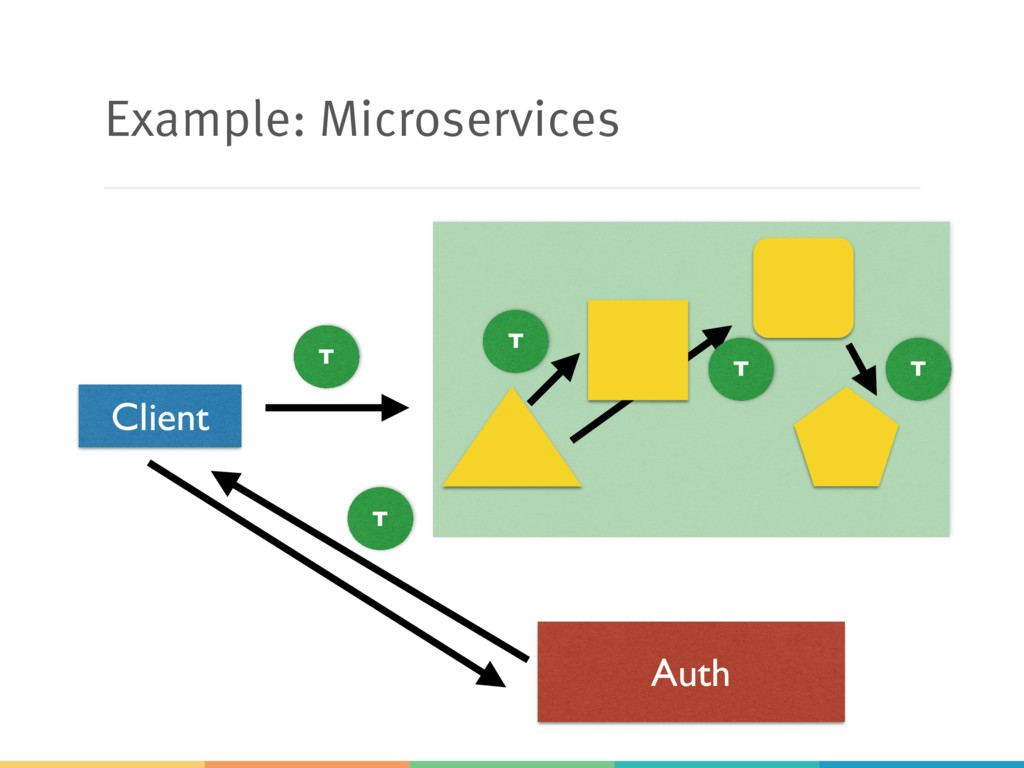
Example: Microservices Client Auth T T T T T
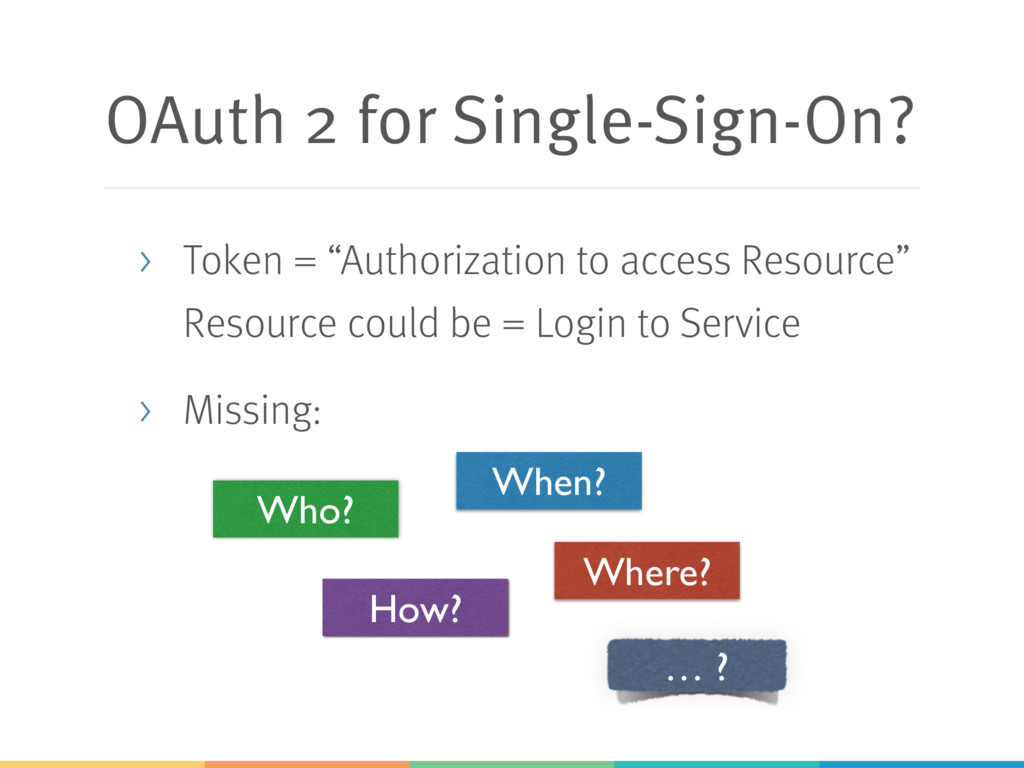
OAuth 2 for Single-Sign-On? > Token = “Authorization to access
Resource” Resource could be = Login to Service > Missing: Who? Where? When? How? … ?
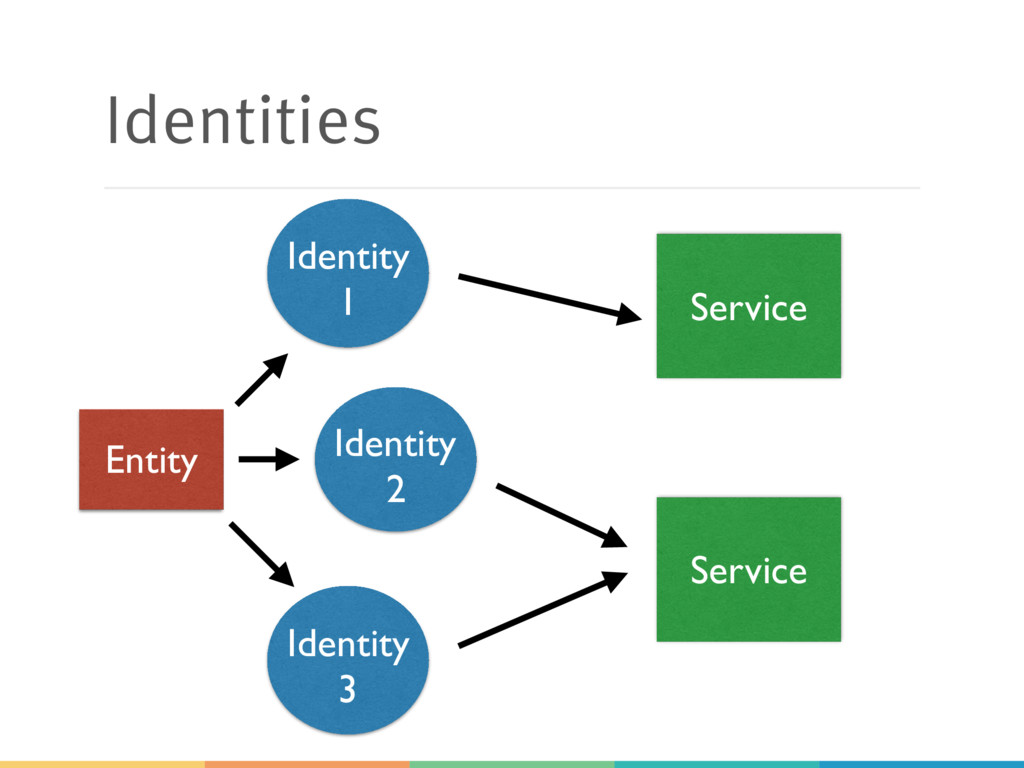
Identities Entity Identity 1 Identity 2 Identity 3 Service Service
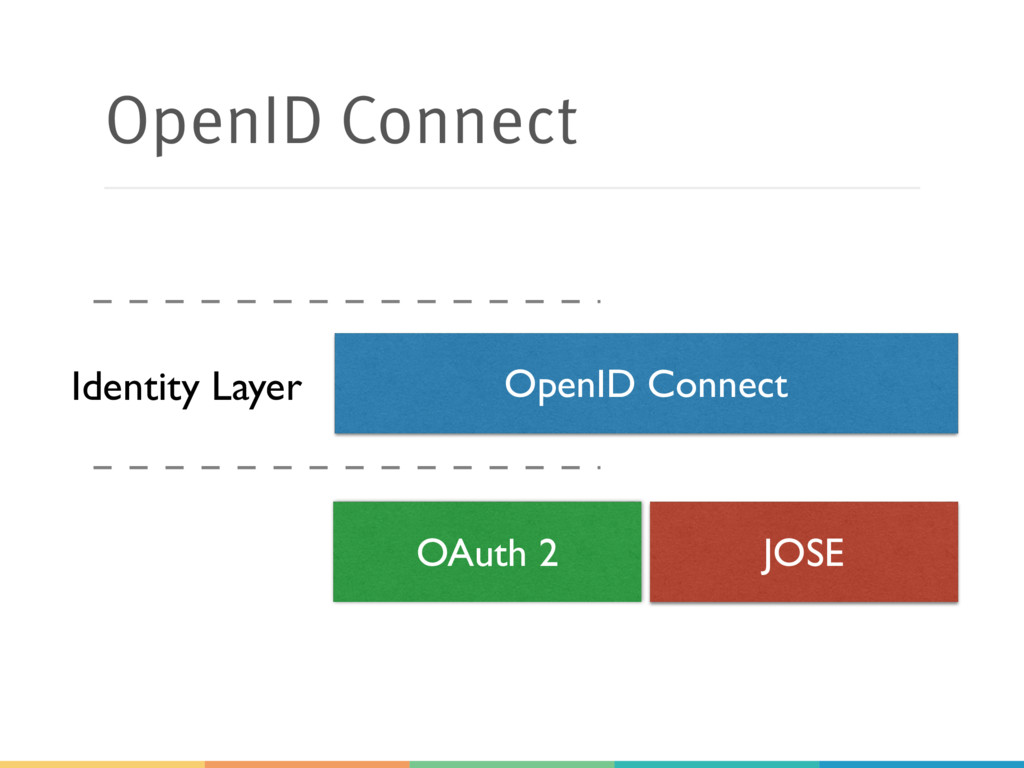
OpenID Connect OAuth 2 JOSE OpenID Connect Identity Layer
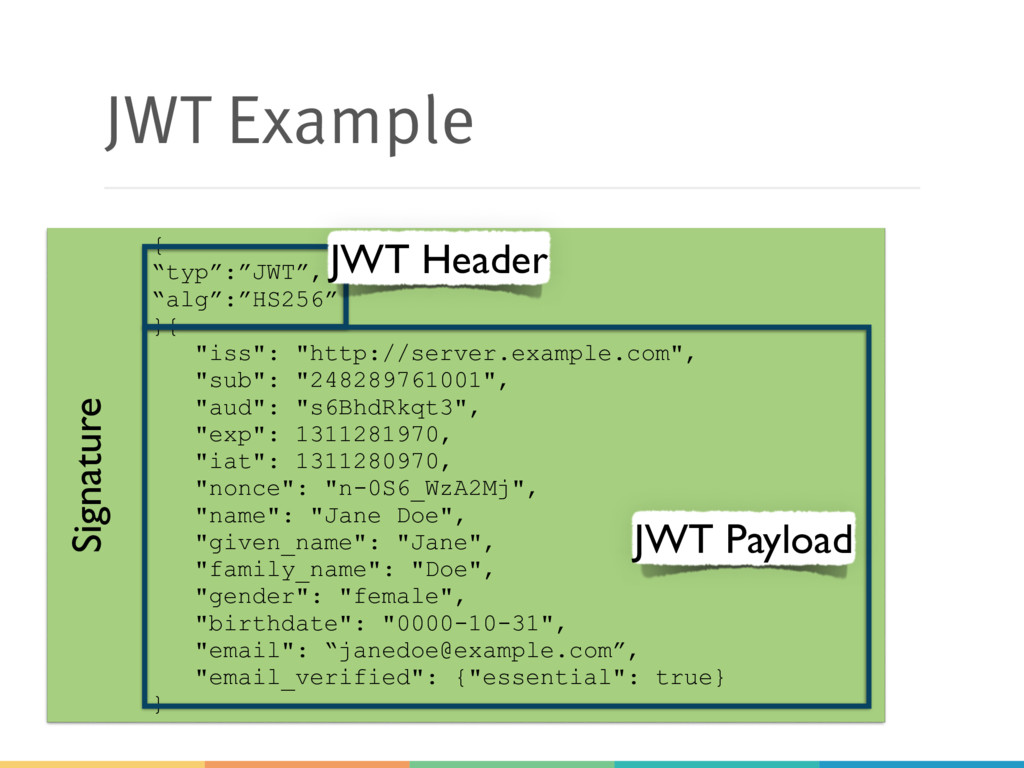
Signature JWT Example { “typ”:”JWT”, “alg”:”HS256” }{ "iss": "http://server.example.com", "sub":
"248289761001", "aud": "s6BhdRkqt3", "exp": 1311281970, "iat": 1311280970, "nonce": "n-0S6_WzA2Mj", "name": "Jane Doe", "given_name": "Jane", "family_name": "Doe", "gender": "female", "birthdate": "0000-10-31", "email": “
[email protected]
”, "email_verified": {"essential": true} } JWT Header JWT Payload
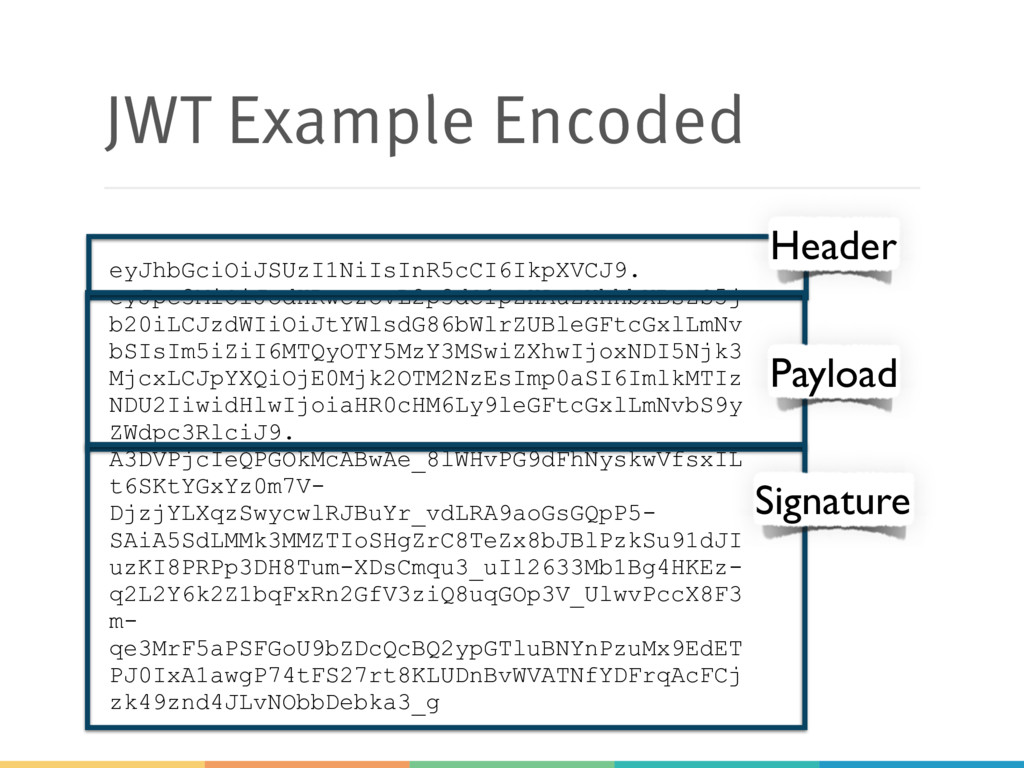
JWT Example Encoded eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9. eyJpc3MiOiJodHRwczovL2p3dC1pZHAuZXhhbXBsZS5j b20iLCJzdWIiOiJtYWlsdG86bWlrZUBleGFtcGxlLmNv bSIsIm5iZiI6MTQyOTY5MzY3MSwiZXhwIjoxNDI5Njk3 MjcxLCJpYXQiOjE0Mjk2OTM2NzEsImp0aSI6ImlkMTIz NDU2IiwidHlwIjoiaHR0cHM6Ly9leGFtcGxlLmNvbS9y ZWdpc3RlciJ9.
A3DVPjcIeQPGOkMcABwAe_8lWHvPG9dFhNyskwVfsxIL t6SKtYGxYz0m7V- DjzjYLXqzSwycwlRJBuYr_vdLRA9aoGsGQpP5- SAiA5SdLMMk3MMZTIoSHgZrC8TeZx8bJBlPzkSu91dJI uzKI8PRPp3DH8Tum-XDsCmqu3_uIl2633Mb1Bg4HKEz- q2L2Y6k2Z1bqFxRn2GfV3ziQ8uqGOp3V_UlwvPccX8F3 m- qe3MrF5aPSFGoU9bZDcQcBQ2ypGTluBNYnPzuMx9EdET PJ0IxA1awgP74tFS27rt8KLUDnBvWVATNfYDFrqAcFCj zk49znd4JLvNObbDebka3_g Header Payload Signature
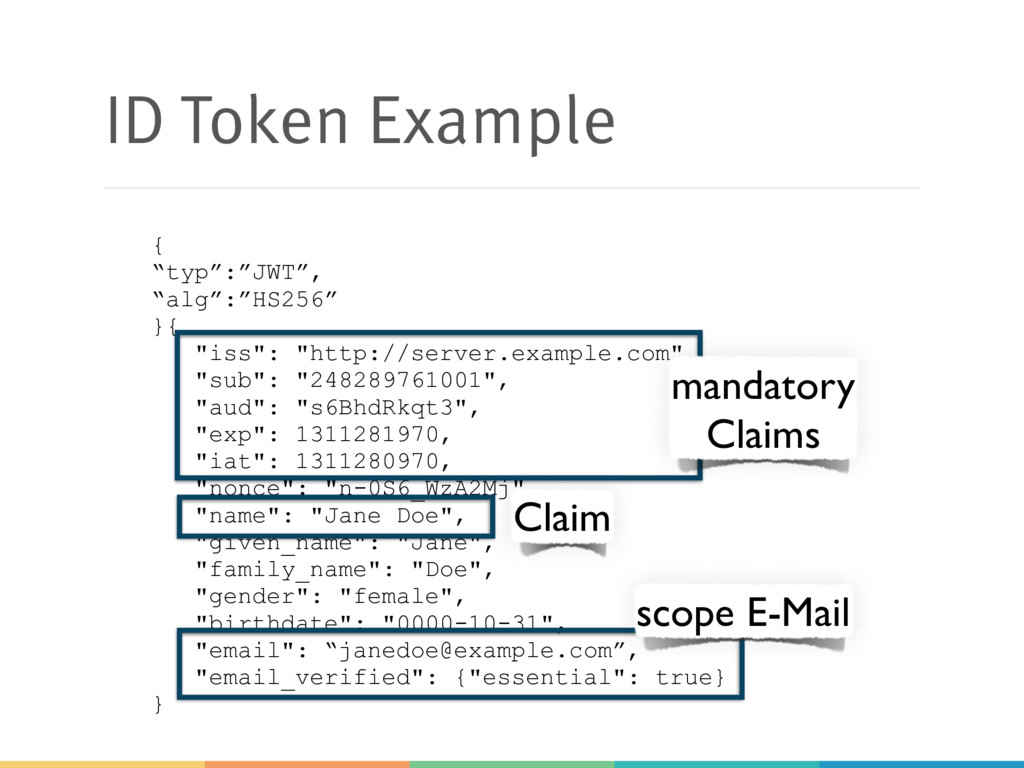
ID Token Example { “typ”:”JWT”, “alg”:”HS256” }{ "iss": "http://server.example.com", "sub":
"248289761001", "aud": "s6BhdRkqt3", "exp": 1311281970, "iat": 1311280970, "nonce": "n-0S6_WzA2Mj", "name": "Jane Doe", "given_name": "Jane", "family_name": "Doe", "gender": "female", "birthdate": "0000-10-31", "email": “
[email protected]
”, "email_verified": {"essential": true} } Claim mandatory Claims scope E-Mail
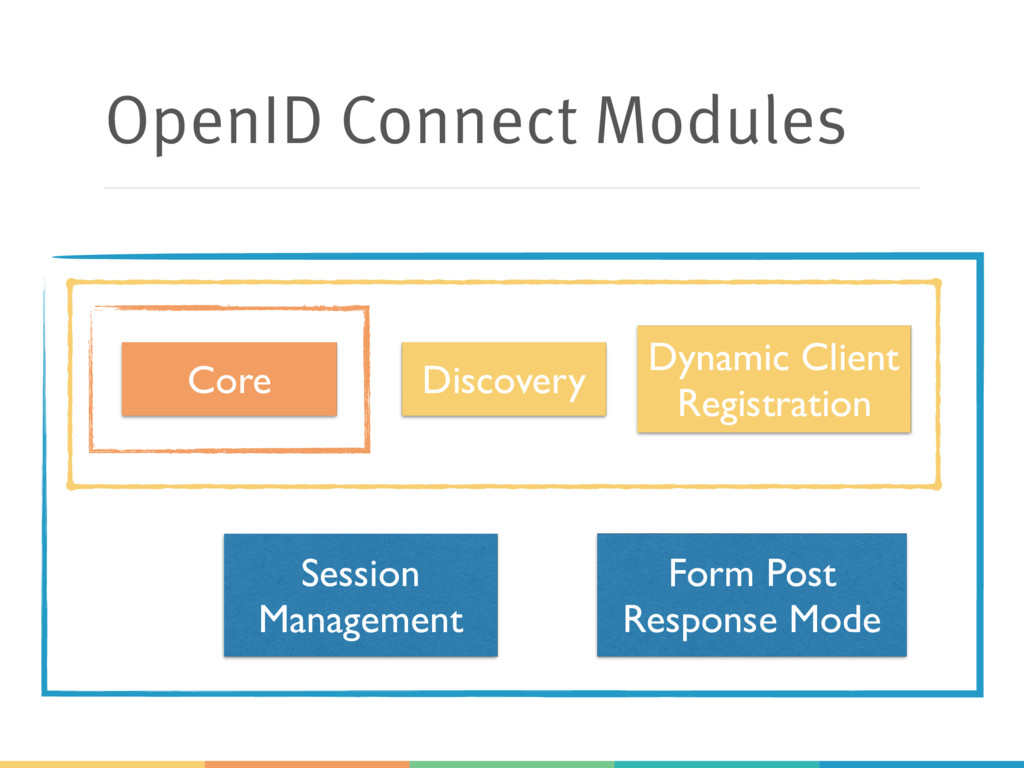
OpenID Connect Modules Core Discovery Dynamic Client Registration Session Management
Form Post Response Mode
Enterprise Use Cases > Securing internal APIs > Single-Sign-On >
Active Directory > Mobile Clients > White Label Software
Should I use it? > OpenID Connect Extensions still
partly Working Drafts > OAuth Extensions: PoP, etc. > Implementation Complexity
Simon Kölsch | @simkoelsch
[email protected]
innoQ Deutschland GmbH Krischerstr. 100
40789 Monheim am Rhein Germany Phone: +49 2173 3366-0 innoQ Schweiz GmbH Gewerbestr. 11 CH-6330 Cham Switzerland Phone: +41 41 743 0116 www.innoq.com Ohlauer Straße 43 10999 Berlin Germany Ludwigstrasse 180 E 63067 Offenbach Germany Kreuzstrasse 16 D-81373 München Germany Thank you! Questions? Comments? Christoph Iserlohn
[email protected]


 simkoelsch
 juanmartin2026
 masakiokuda
 bvr7352
 suisan
 uchi8977
 yatabe
 matleenalaakso
 signer
 robintux
 naoji_taniguchi_ksk_0827
 cassininazir
 427marketing
 gr2m
 sachag
 tammyeverts
 kastner
 3n
 scottboms
 axbom
 marcduiker
 michielstock
 baasie