Share
Embed
Transcript
20 slides
-
The attacks • Insufficient Transport Layer Protection • SQL Injection
• Cross-Site Scripting (XSS) • Cross-Site Request Forgery (CSRF) -
Django - enabling HTTPS ๏ Quite complicated to enable it
on the development server http://stackoverflow.com/questions/8023126/how-can-i-test-https-connections-with-django-as-easily-as-i-can-non-https-connec ✓ More easier when used with a “real” web server (Apache) ➡ See the forthcoming lecture on “Deploying a Django app” -
General Good Practices You application should not mix http and
https URLs related to your domain ➡ Never hard encode URLs in your templates or static documents -
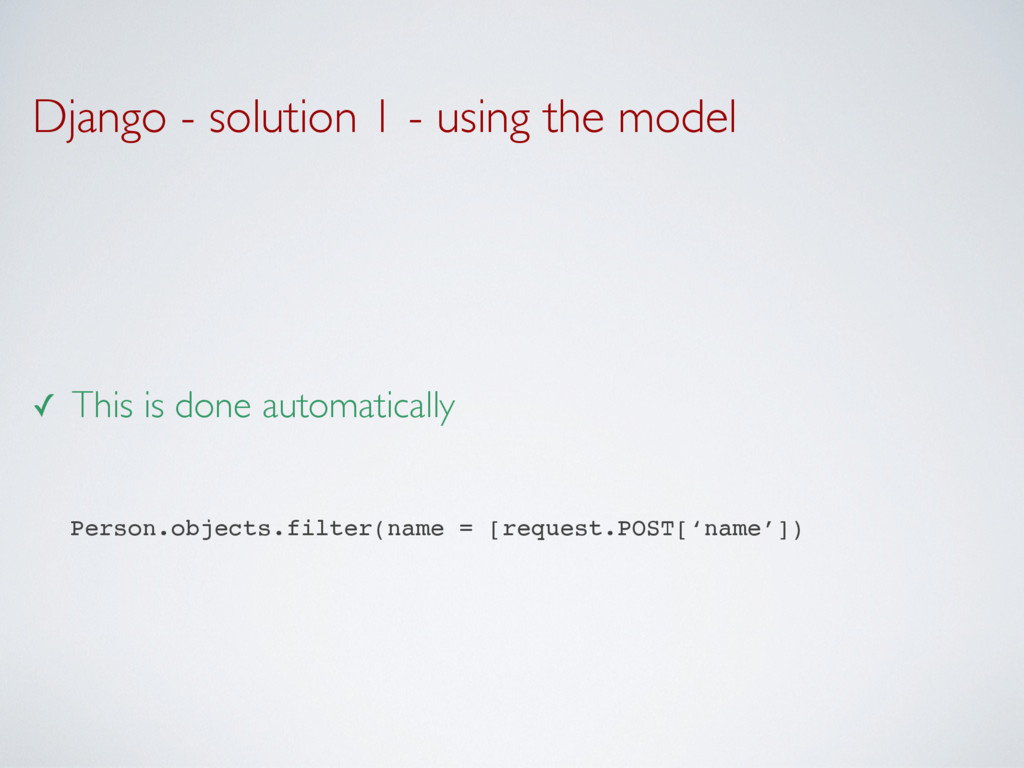
Django - solution 1 - using the model ✓ This
is done automatically Person.objects.filter(name = [request.POST[‘name’]) -
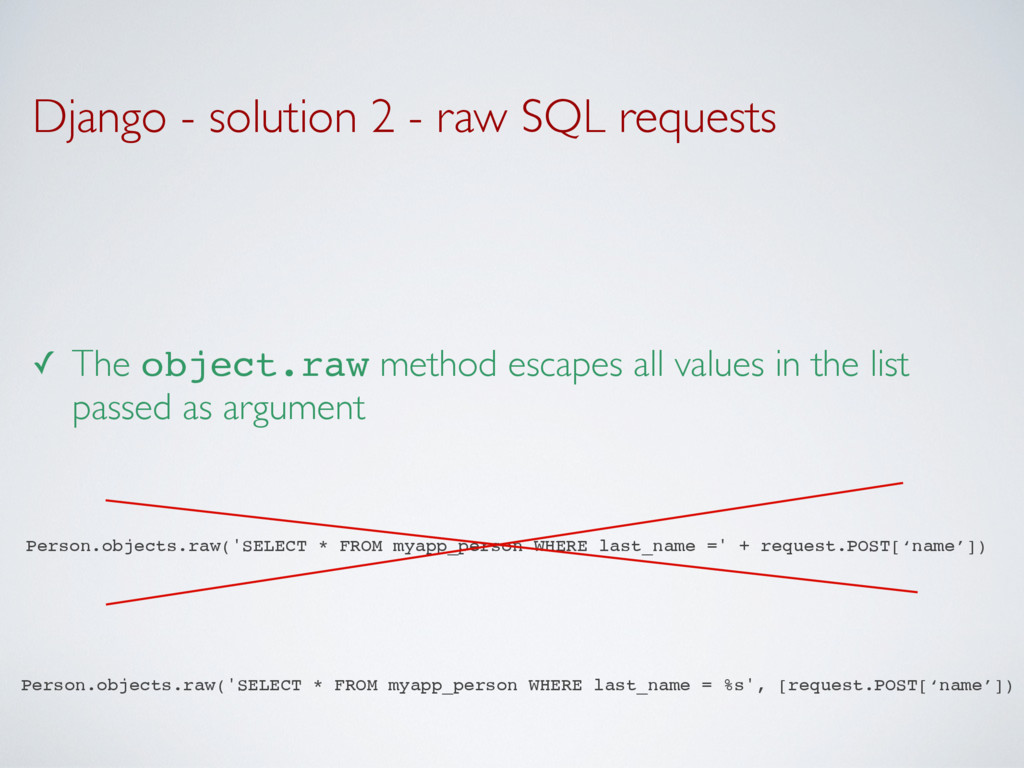
Django - solution 2 - raw SQL requests ✓ The
object.raw method escapes all values in the list passed as argument Person.objects.raw('SELECT * FROM myapp_person WHERE last_name = %s', [request.POST[‘name’]) Person.objects.raw('SELECT * FROM myapp_person WHERE last_name =' + request.POST[‘name’]) -
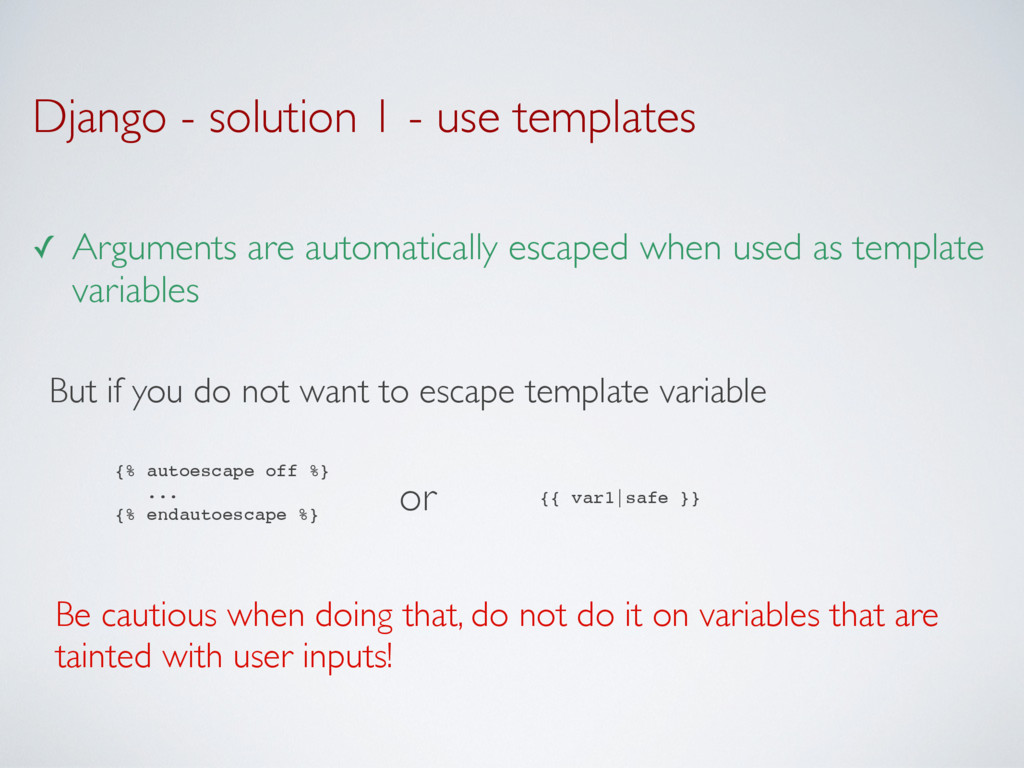
Django - solution 1 - use templates ✓ Arguments are
automatically escaped when used as template variables {% autoescape off %} ... {% endautoescape %} {{ var1|safe }} Be cautious when doing that, do not do it on variables that are tainted with user inputs! But if you do not want to escape template variable or -
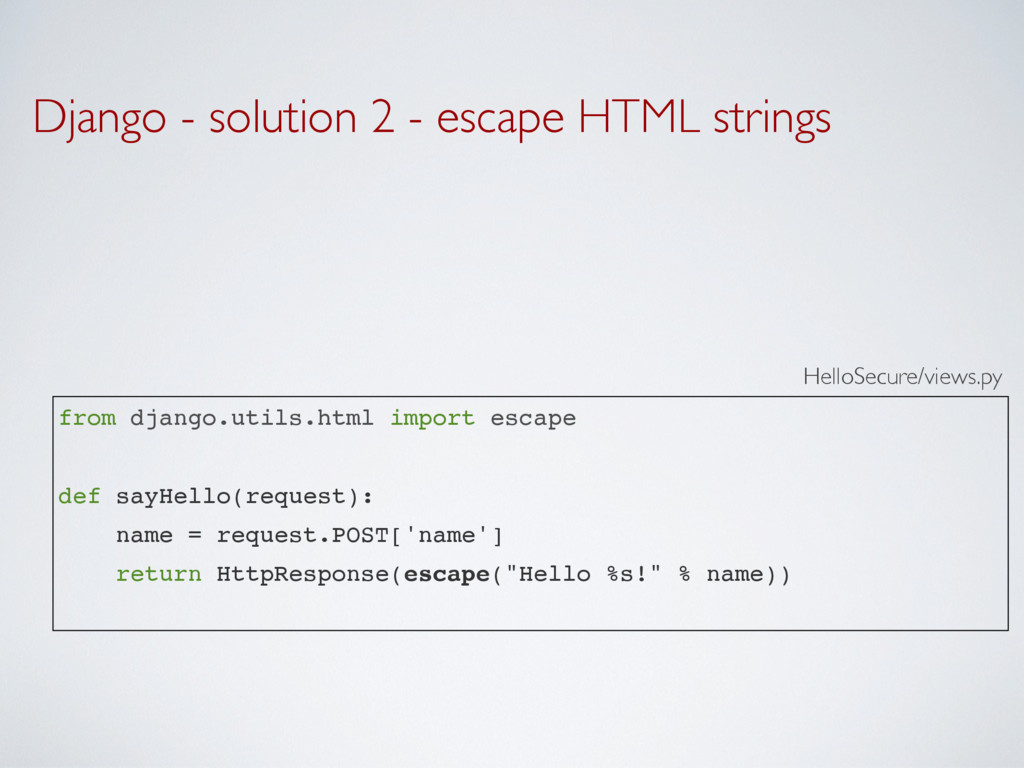
Django - solution 2 - escape HTML strings from django.utils.html
import escape def sayHello(request): name = request.POST['name'] return HttpResponse(escape("Hello %s!" % name)) HelloSecure/views.py -
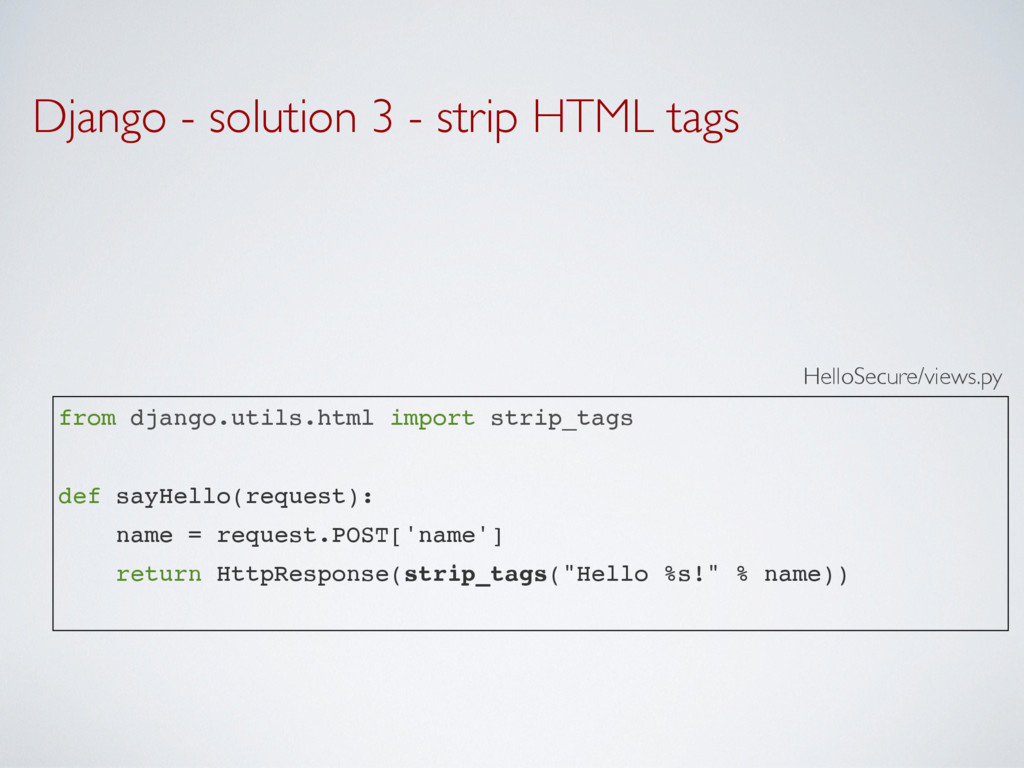
Django - solution 3 - strip HTML tags from django.utils.html
import strip_tags def sayHello(request): name = request.POST['name'] return HttpResponse(strip_tags("Hello %s!" % name)) HelloSecure/views.py -
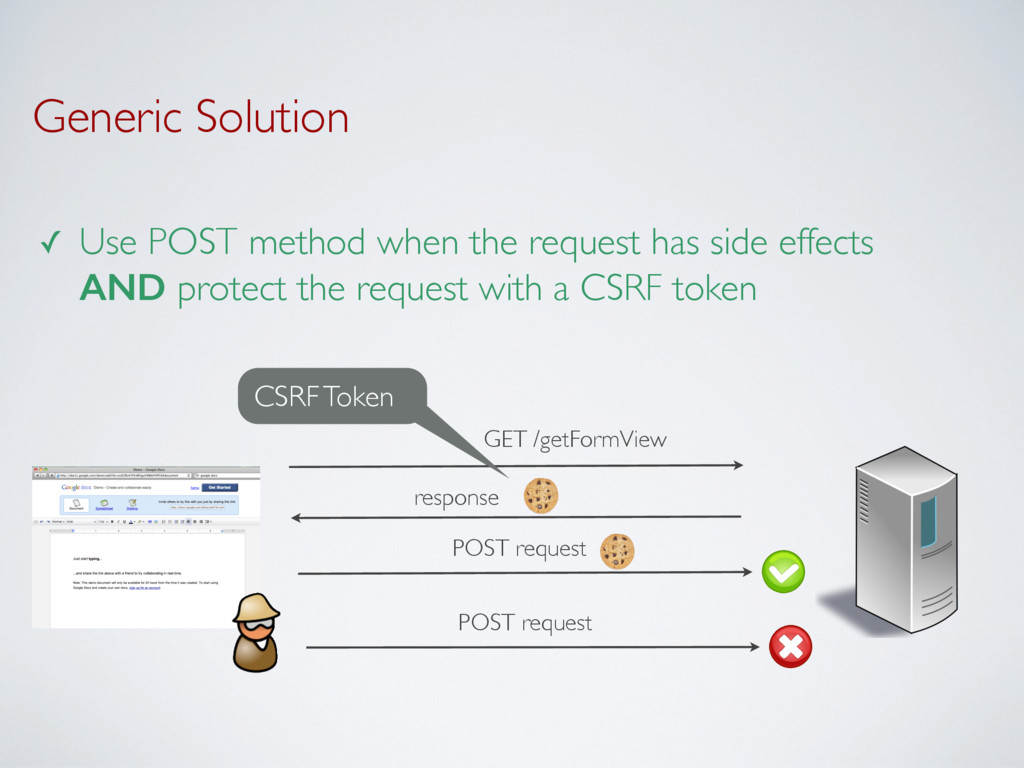
Generic Solution ✓ Use POST method when the request has
side effects AND protect the request with a CSRF token GET /getFormView response POST request CSRF Token POST request -
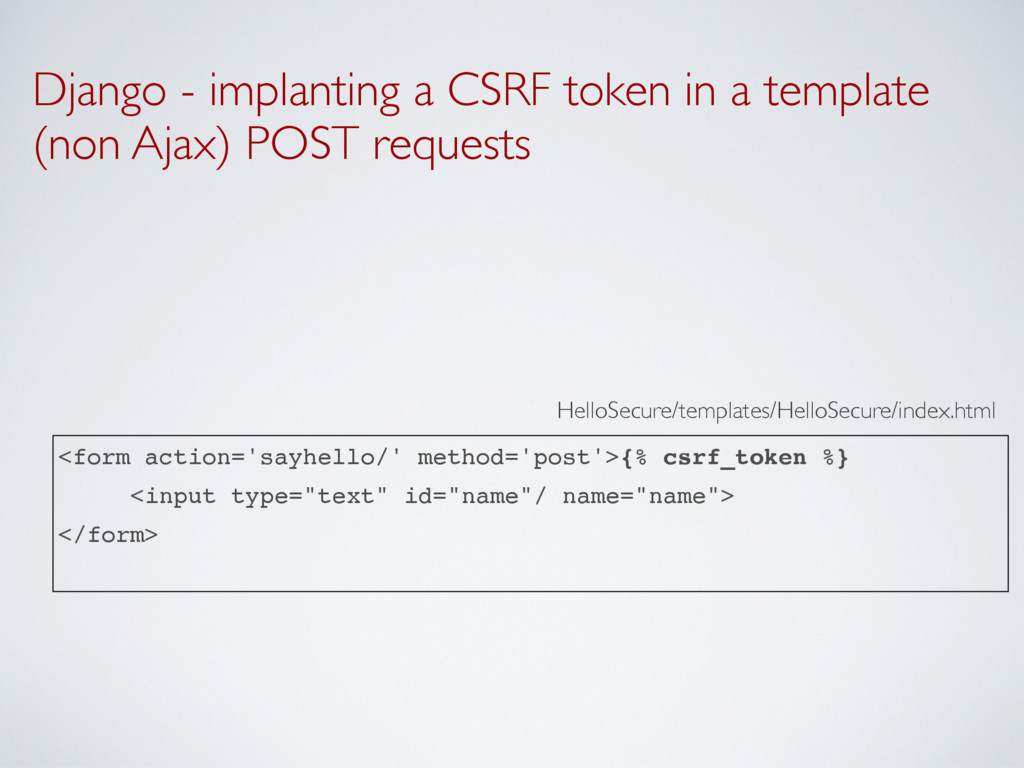
Django - implanting a CSRF token in a template (non
Ajax) POST requests <form action='sayhello/' method='post'>{% csrf_token %} <input type="text" id="name"/ name="name"> </form> HelloSecure/templates/HelloSecure/index.html -
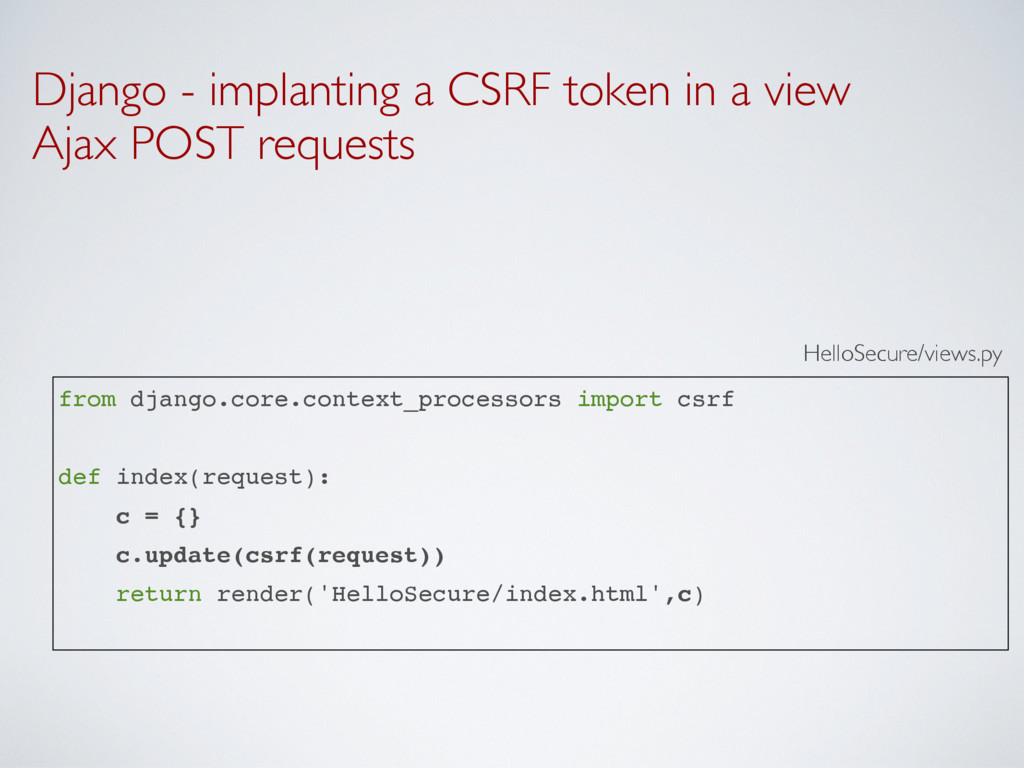
Django - implanting a CSRF token in a view Ajax
POST requests from django.core.context_processors import csrf def index(request): c = {} c.update(csrf(request)) return render('HelloSecure/index.html',c) HelloSecure/views.py -
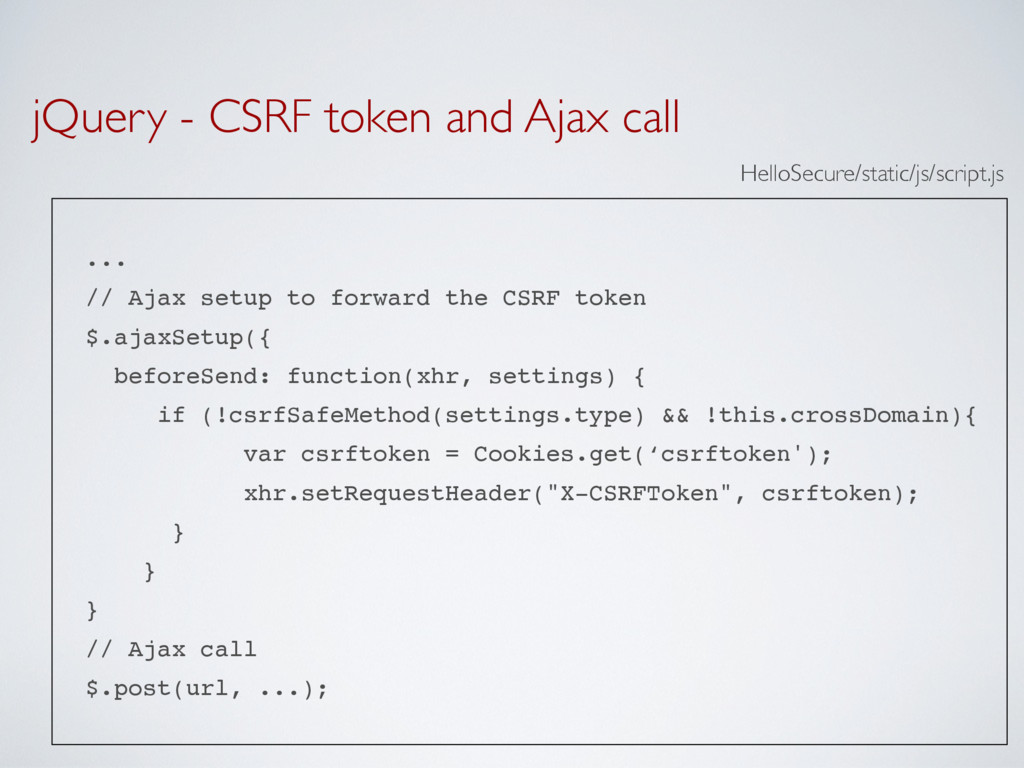
jQuery - CSRF token and Ajax call ... // Ajax
setup to forward the CSRF token $.ajaxSetup({ beforeSend: function(xhr, settings) { if (!csrfSafeMethod(settings.type) && !this.crossDomain){ var csrftoken = Cookies.get(‘csrftoken'); xhr.setRequestHeader("X-CSRFToken", csrftoken); } } } // Ajax call $.post(url, ...); HelloSecure/static/js/script.js -
Be careful ! ➡ X-CSRF headers prevents from cross-site requests
only ๏ But not same-origin requests (as shown in class) ✓ Solution - disable GET requests for POST services -
Django - require_http_methods from django.views.decorators.http import require_http_methods @require_http_methods(["POST"]) def sayHello(request):
name = request.POST['name'] return HttpResponse(escape("Hello %s!" % name))