Share
Embed
CSCD27 Introduction
ThierrySans
September 12, 2016
Transcript
36 slides
-
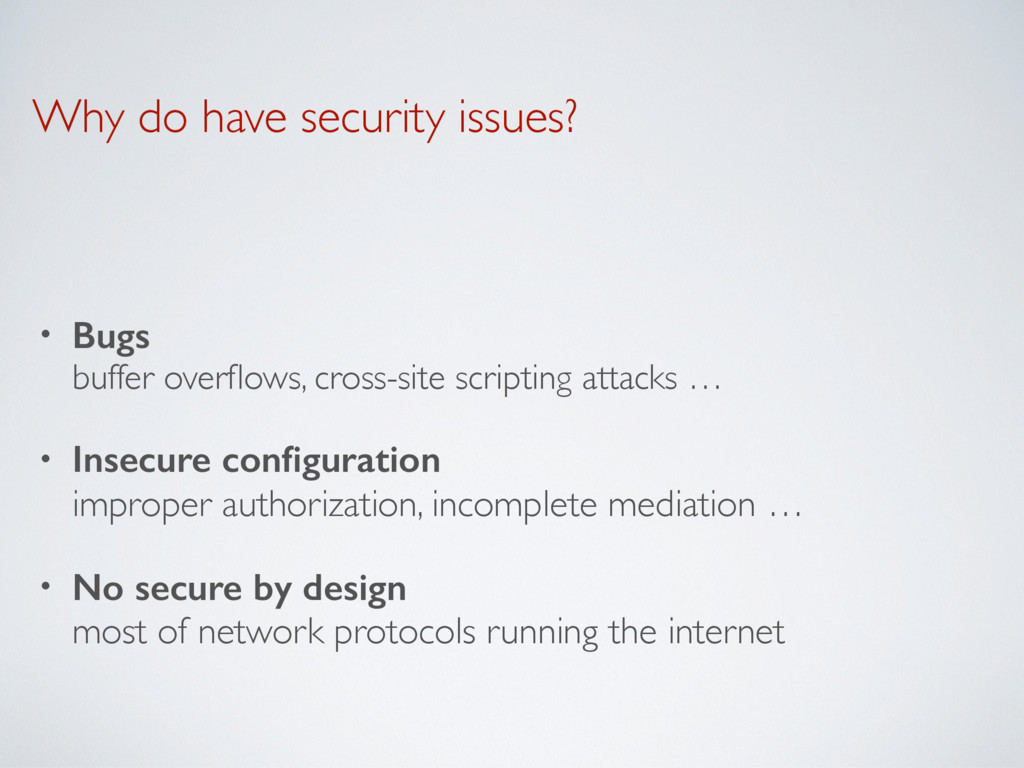
Why do have security issues? • Bugs buffer overflows, cross-site
scripting attacks … • Insecure configuration improper authorization, incomplete mediation … • No secure by design most of network protocols running the internet -
Why security should matters to you? • Because you are
going to build computer systems, networks and software -
Legacy • CSCD27 Computer and Network Security Alan Rosselet University
of Toronto Scarborough • 15-349 Introduction to Computer and Network Security Iliano Cervesato, Khaled Harras and Thierry Sans Carnegie Mellon University Qatar -
Course Objectives SCSD27 is an undergraduate course that provides a
theoretical and technical overview of the field of computer security -
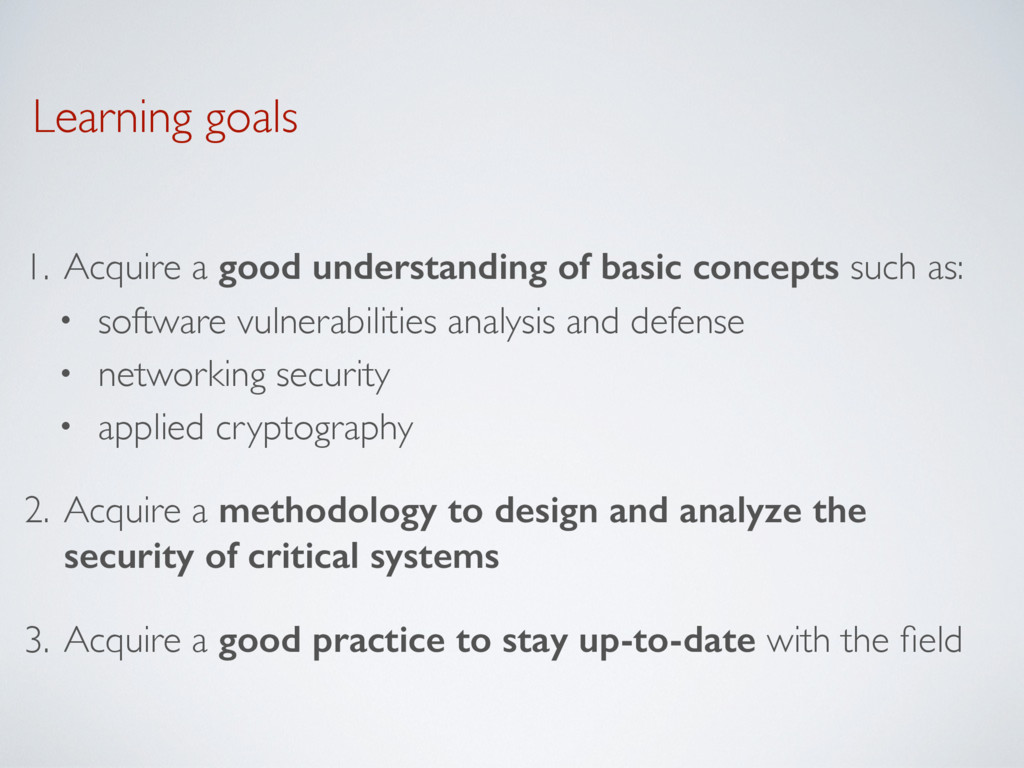
Learning goals 1. Acquire a good understanding of basic concepts
such as: • software vulnerabilities analysis and defense • networking security • applied cryptography 2. Acquire a methodology to design and analyze the security of critical systems 3. Acquire a good practice to stay up-to-date with the field -
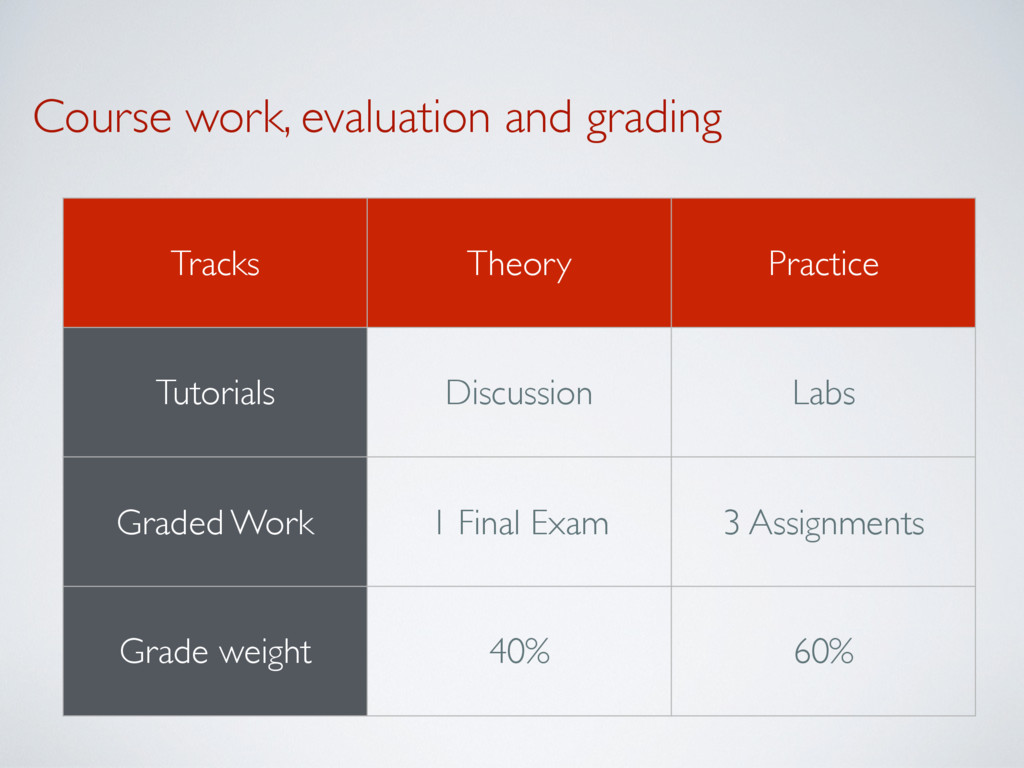
Course work, evaluation and grading Tracks Theory Practice Tutorials Discussion
Labs Graded Work 1 Final Exam 3 Assignments Grade weight 40% 60% -
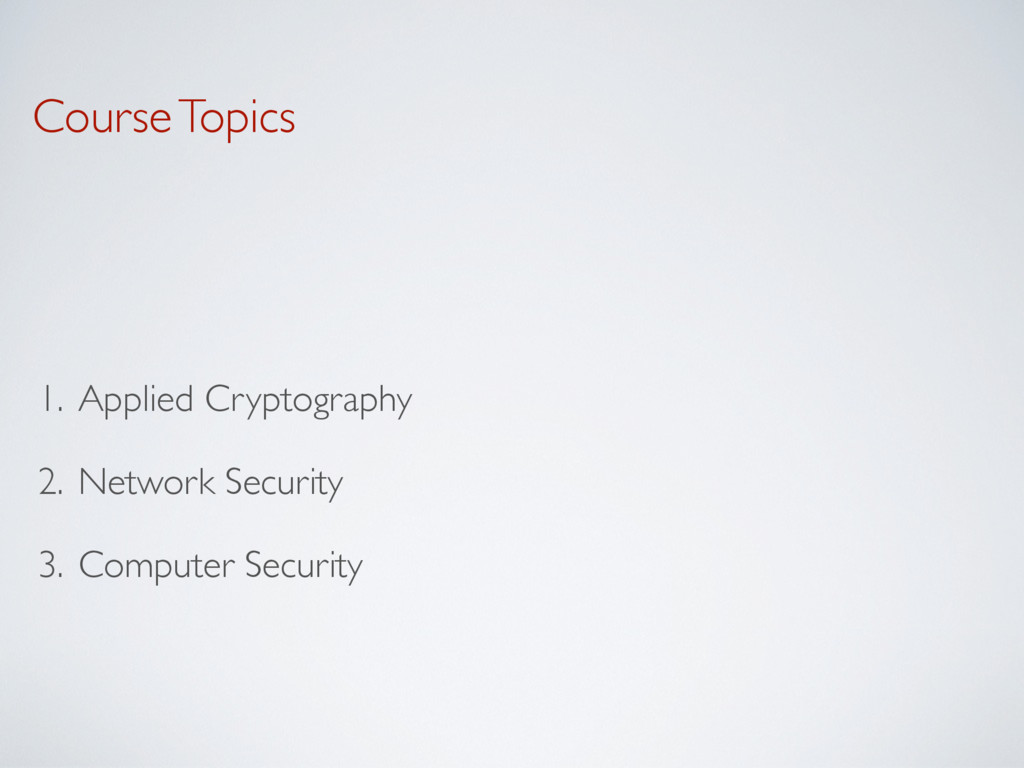
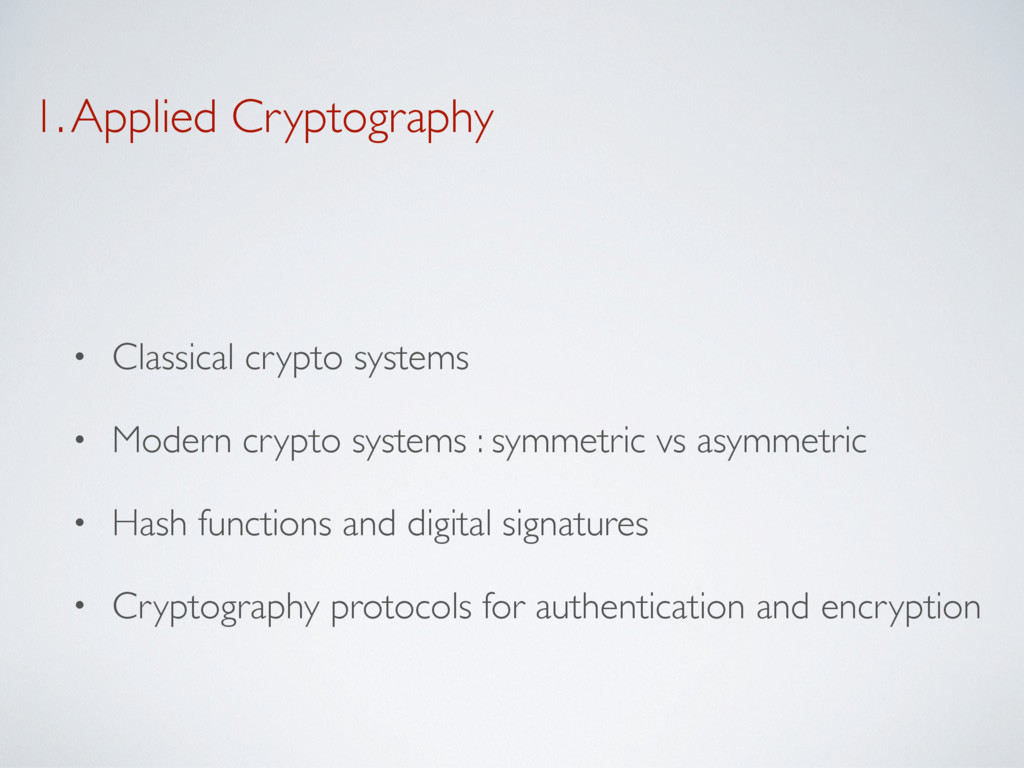
1. Applied Cryptography • Classical crypto systems • Modern crypto
systems : symmetric vs asymmetric • Hash functions and digital signatures • Cryptography protocols for authentication and encryption -
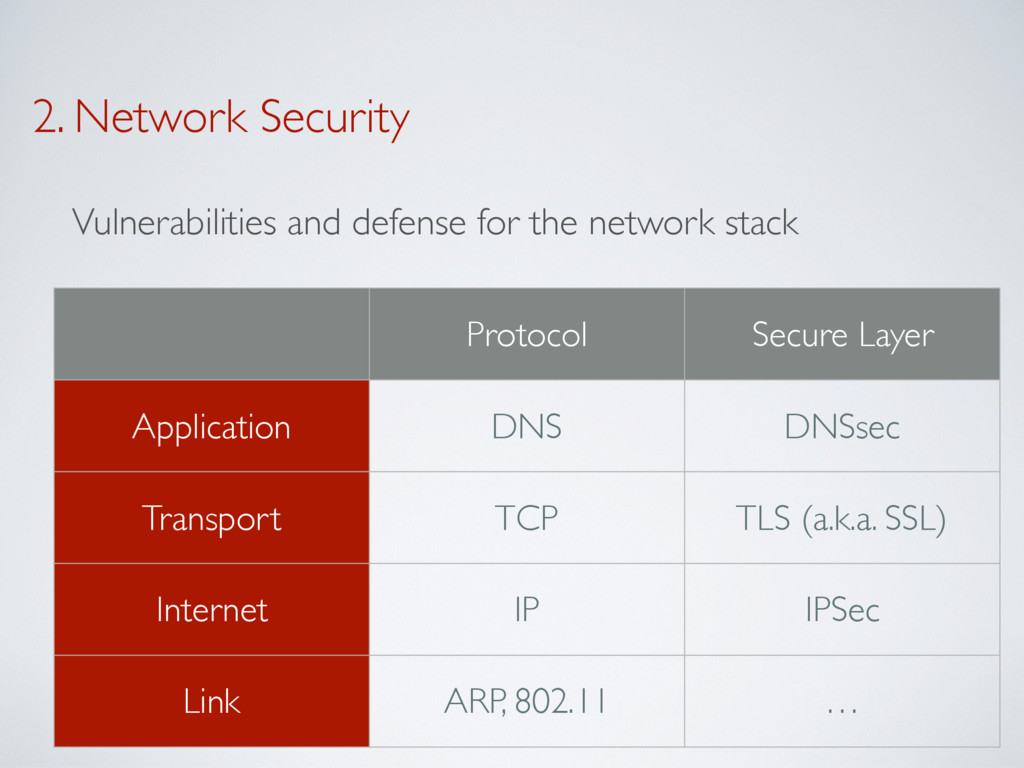
2. Network Security Vulnerabilities and defense for the network stack
Protocol Secure Layer Application DNS DNSsec Transport TCP TLS (a.k.a. SSL) Internet IP IPSec Link ARP, 802.11 … -
3. Computer Security • Operating Systems • Programs • Malicious
code • Email and Web -
Ethical Hacking • You will be exposed to attack methods
• You should uphold to a high standard of professional and personal ethic • Your knowledge of attack methods does not imply permission to exploit them … even if it seems “harmful fun” • UofT policies are strictly enforced • Canadian Criminal Code is strictly enforced -
How to succeed in this course • Come to lectures,
tutorials … blah blah blah • Do the work … blah blah blah • Be curious, be stubborn and get your hands dirty -
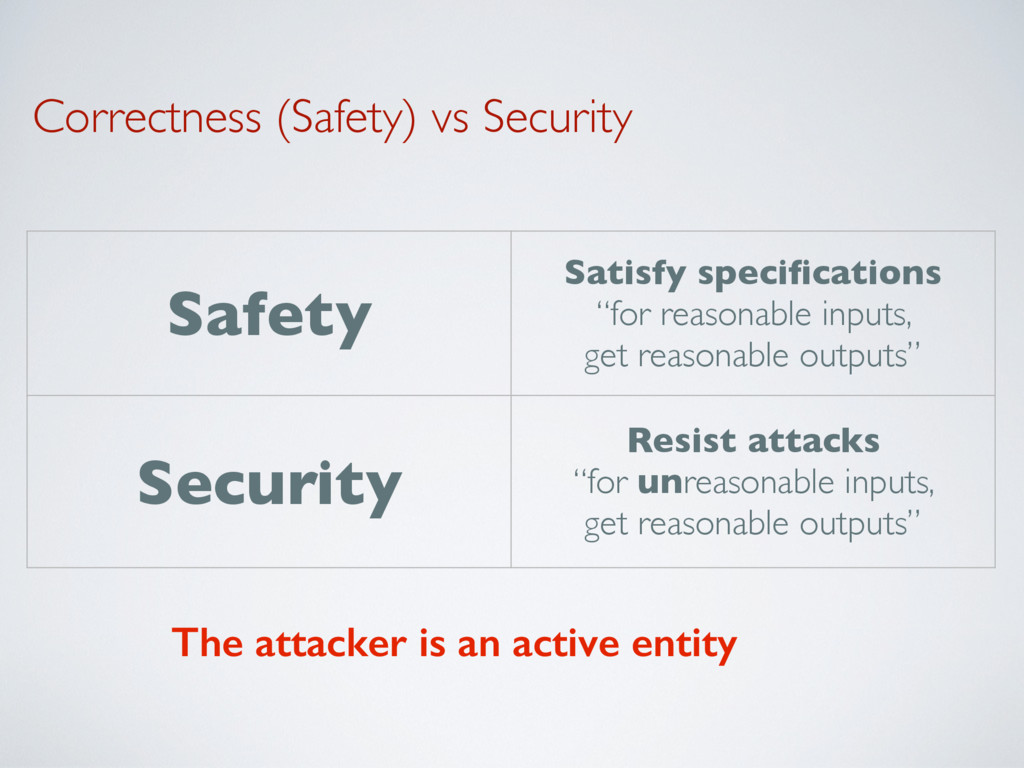
Correctness (Safety) vs Security Safety Satisfy specifications “for reasonable inputs,
get reasonable outputs” Security Resist attacks “for unreasonable inputs, get reasonable outputs” The attacker is an active entity -
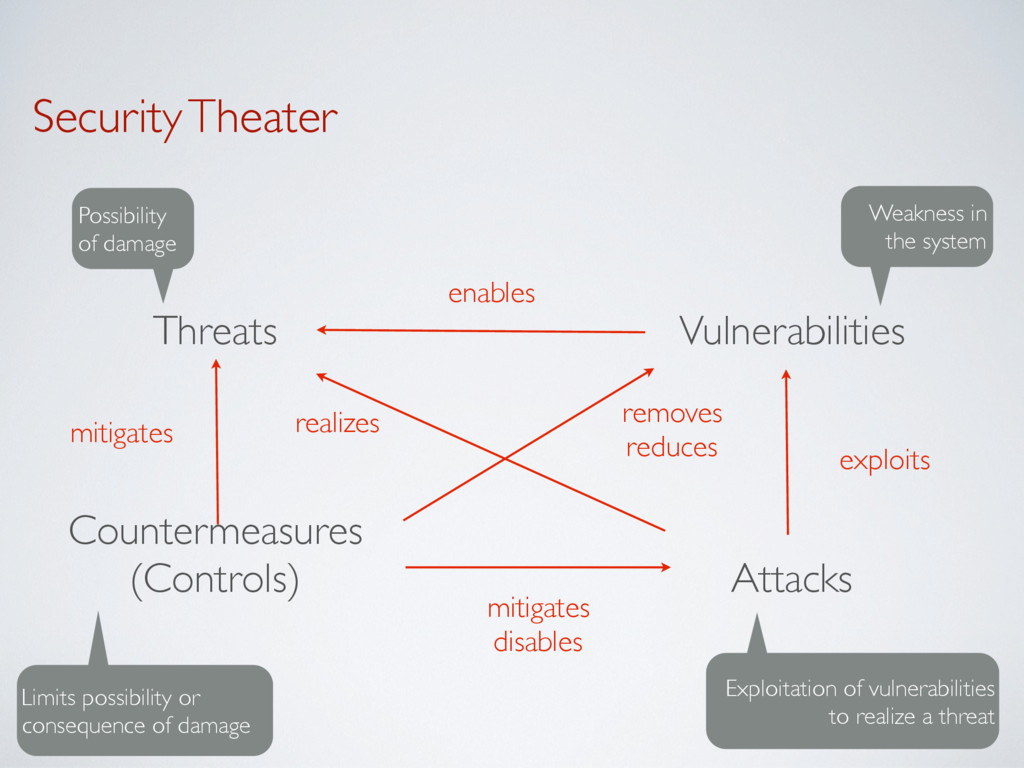
Security Theater Threats Possibility of damage Vulnerabilities Weakness in the
system Attacks Exploitation of vulnerabilities to realize a threat Countermeasures (Controls) Limits possibility or consequence of damage enables exploits mitigates disables mitigates removes reduces realizes -
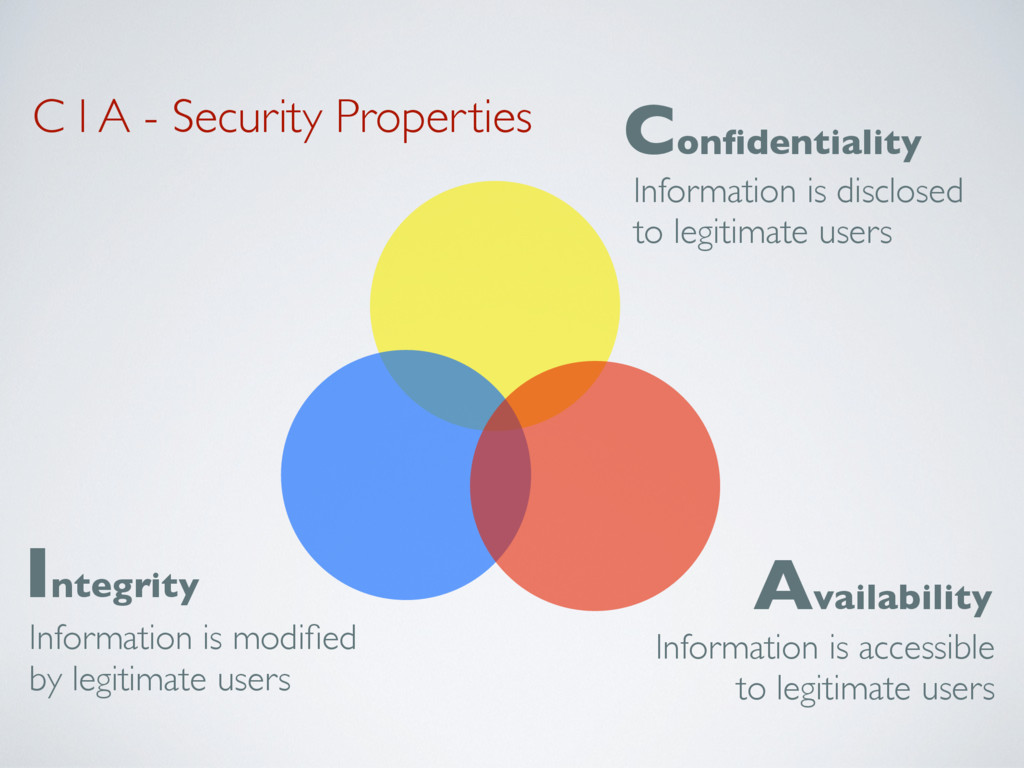
C I A - Security Properties Confidentiality Information is disclosed
to legitimate users Integrity Information is modified by legitimate users Information is accessible to legitimate users Availability -
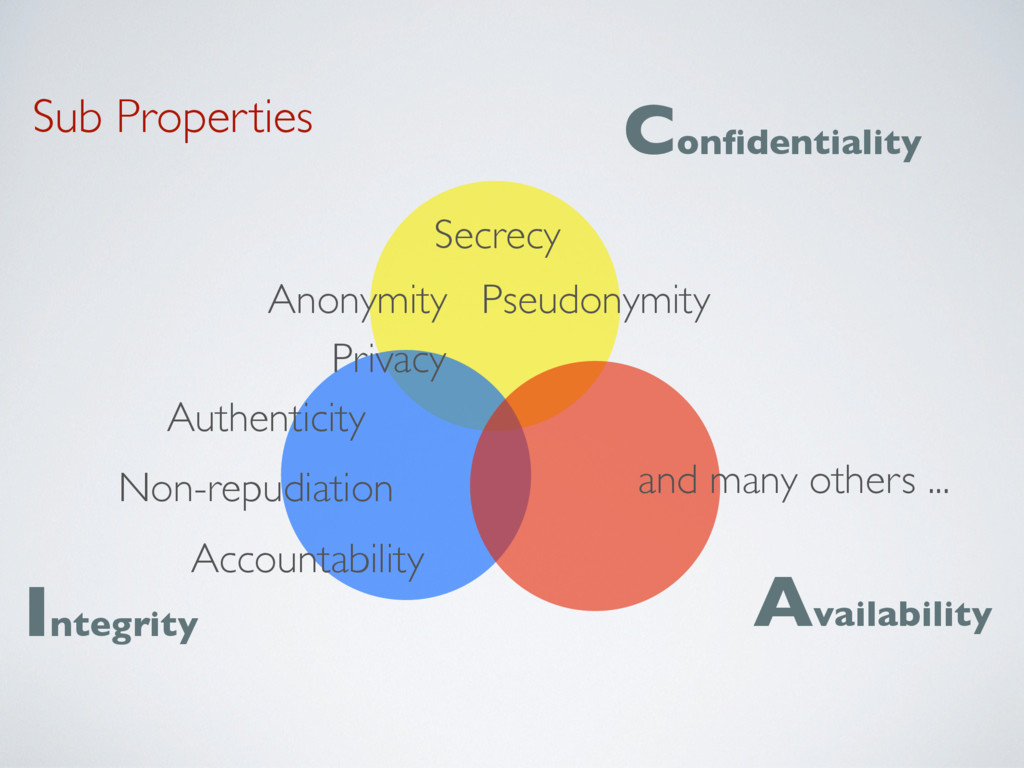
Sub Properties Confidentiality Integrity Availability Secrecy Privacy Pseudonymity Anonymity Authenticity
Non-repudiation Accountability and many others ... -
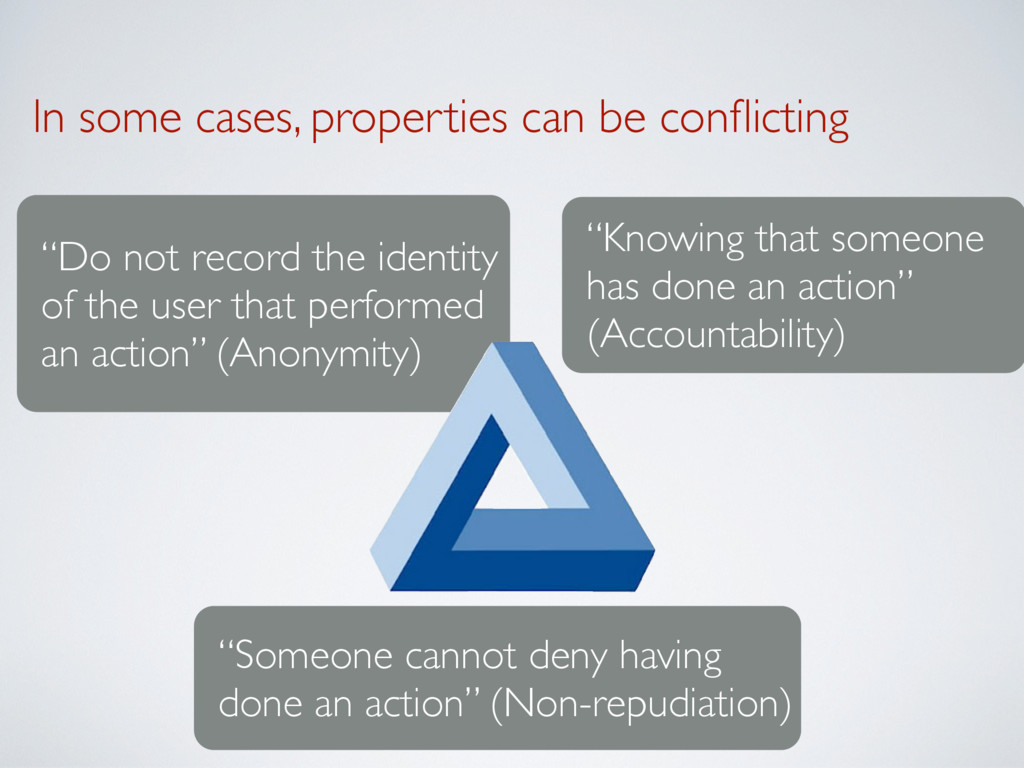
In some cases, properties can be conflicting “Do not record
the identity of the user that performed an action” (Anonymity) “Knowing that someone has done an action” (Accountability) “Someone cannot deny having done an action” (Non-repudiation) -
Dealing with security ✓ Security is often a compromised ✓
Security is engineered -
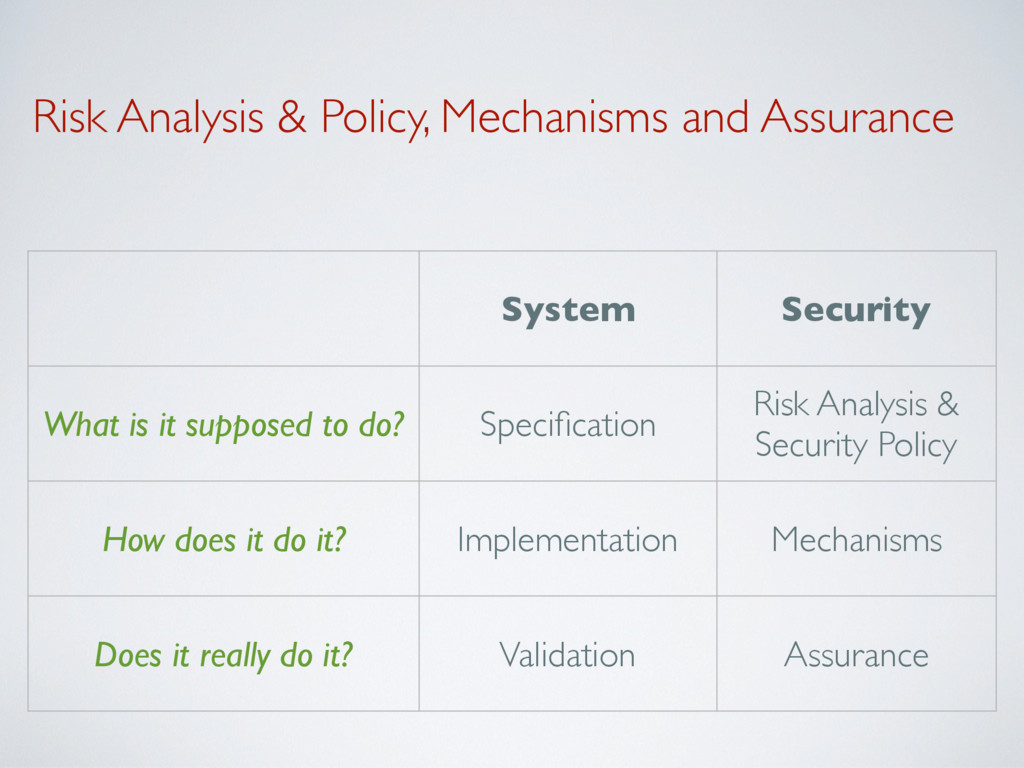
Risk Analysis & Policy, Mechanisms and Assurance System Security What
is it supposed to do? Specification Risk Analysis & Security Policy How does it do it? Implementation Mechanisms Does it really do it? Validation Assurance -
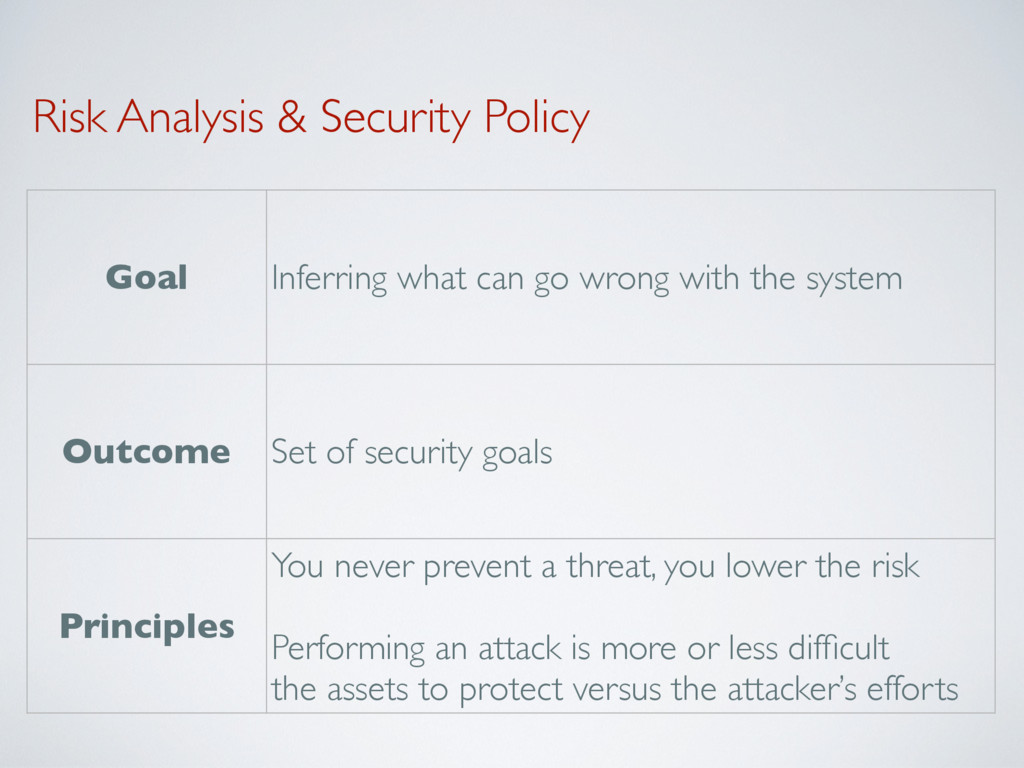
Risk Analysis & Security Policy Goal Inferring what can go
wrong with the system Outcome Set of security goals Principles You never prevent a threat, you lower the risk Performing an attack is more or less difficult the assets to protect versus the attacker’s efforts -
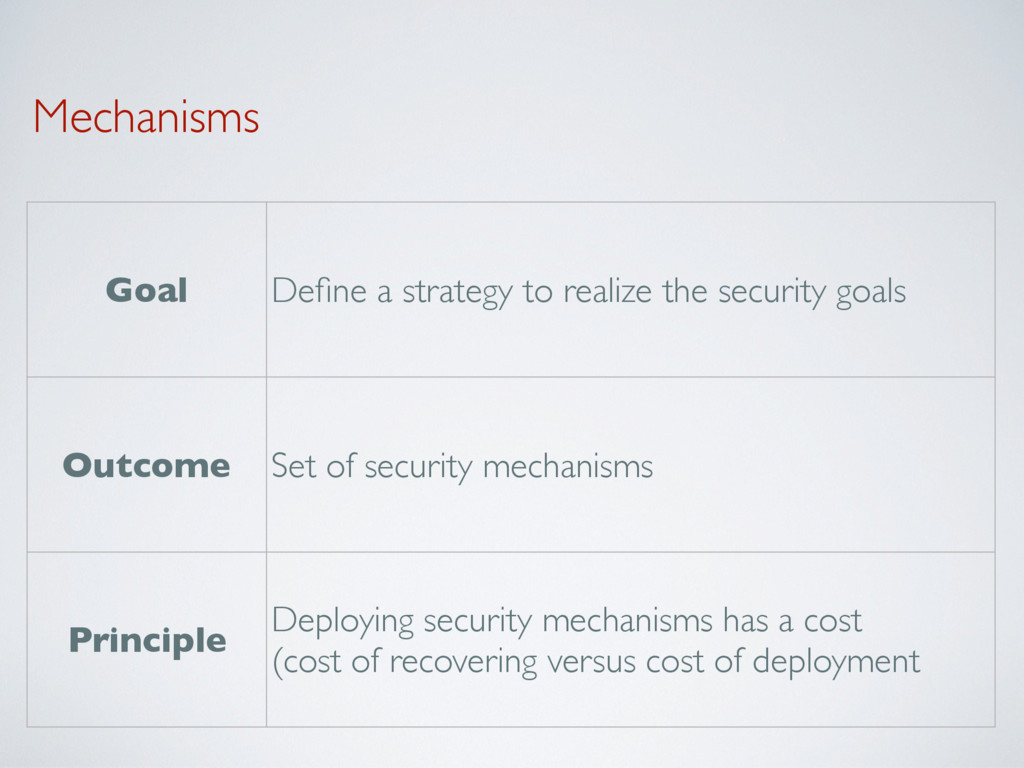
Mechanisms Goal Define a strategy to realize the security goals
Outcome Set of security mechanisms Principle Deploying security mechanisms has a cost (cost of recovering versus cost of deployment -
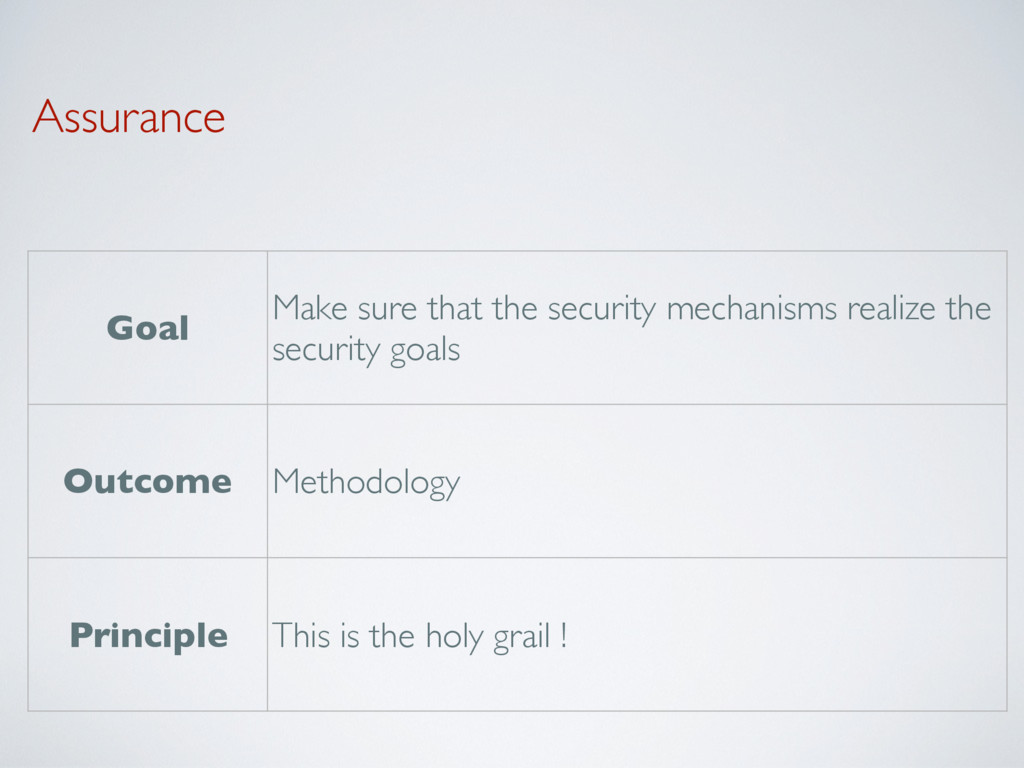
Assurance Goal Make sure that the security mechanisms realize the
security goals Outcome Methodology Principle This is the holy grail !