move user funds • App, that stores sensitive user information on device • Apps, that need to protect in-app purchases on device • Games • Apps, that need to protect Intellectual Property
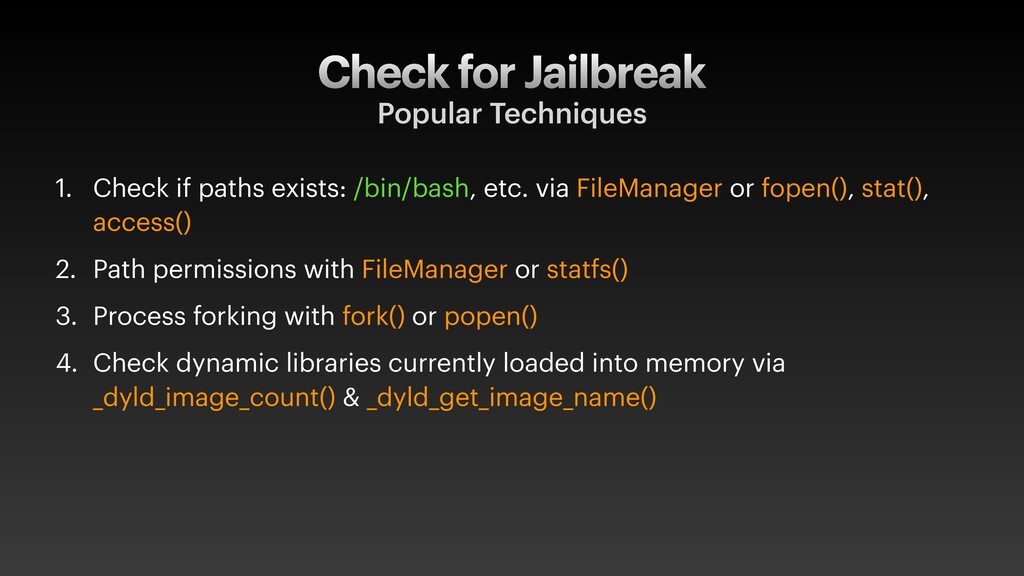
/bin/bash, etc. via FileManager or fopen(), stat(), access() 2. Path permissions with FileManager or statfs() 3. Process forking with fork() or popen() 4. Check dynamic libraries currently loaded into memory via _dyld_image_count() & _dyld_get_image_name()
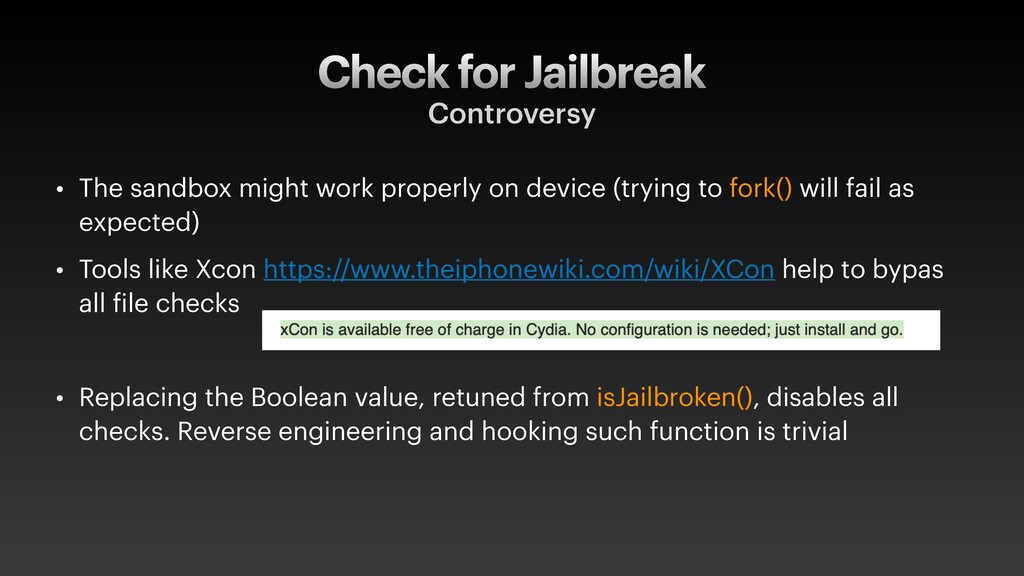
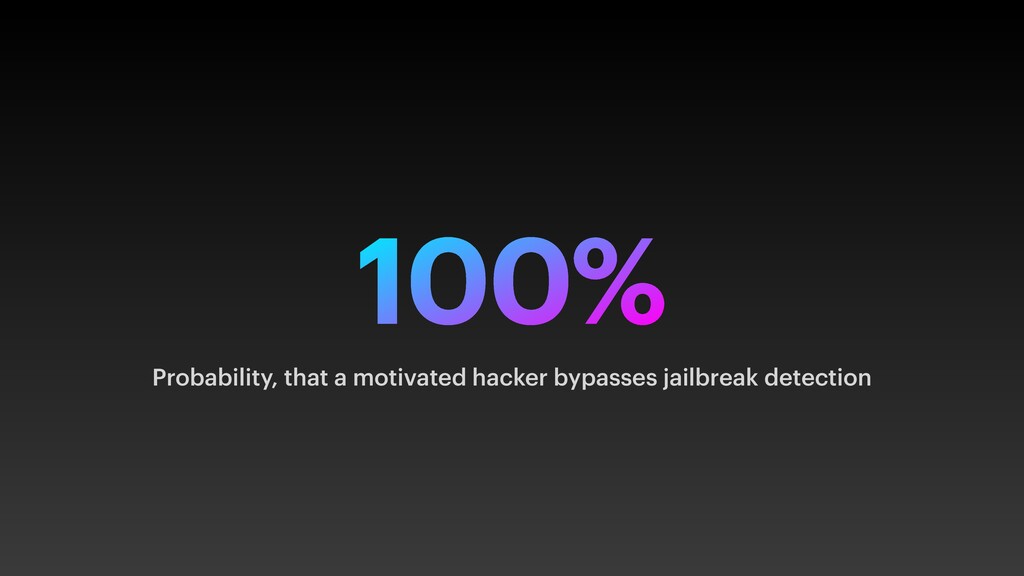
on device (trying to fork() will fail as expected) • Tools like Xcon https://www.theiphonewiki.com/wiki/XCon help to bypas all file checks • Replacing the Boolean value, retuned from isJailbroken(), disables all checks. Reverse engineering and hooking such function is trivial
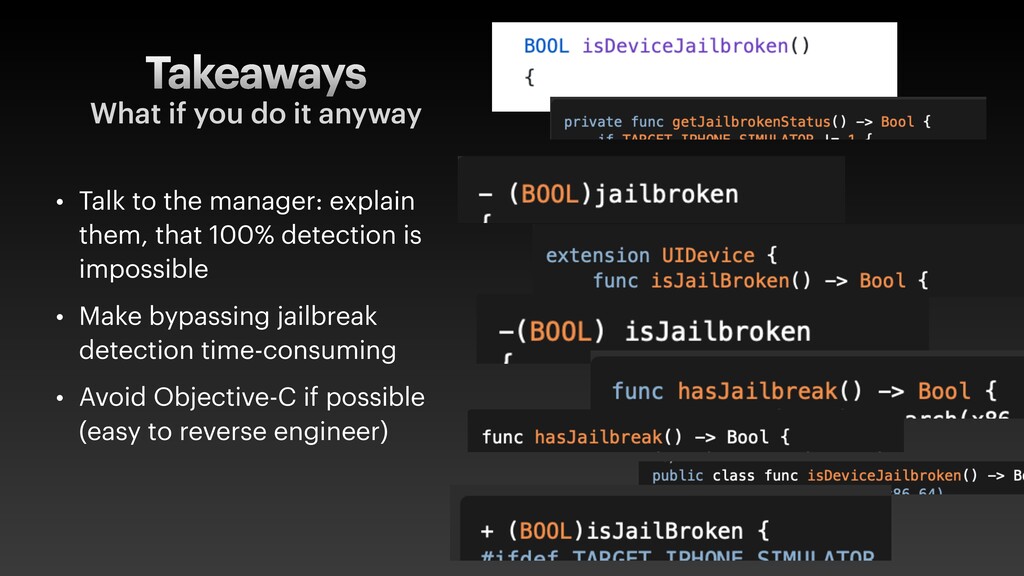
detection is impossible • Make bypassing jailbreak detection time-consuming • Avoid Objective-C if possible (easy to reverse engineer) What if you do it anyway
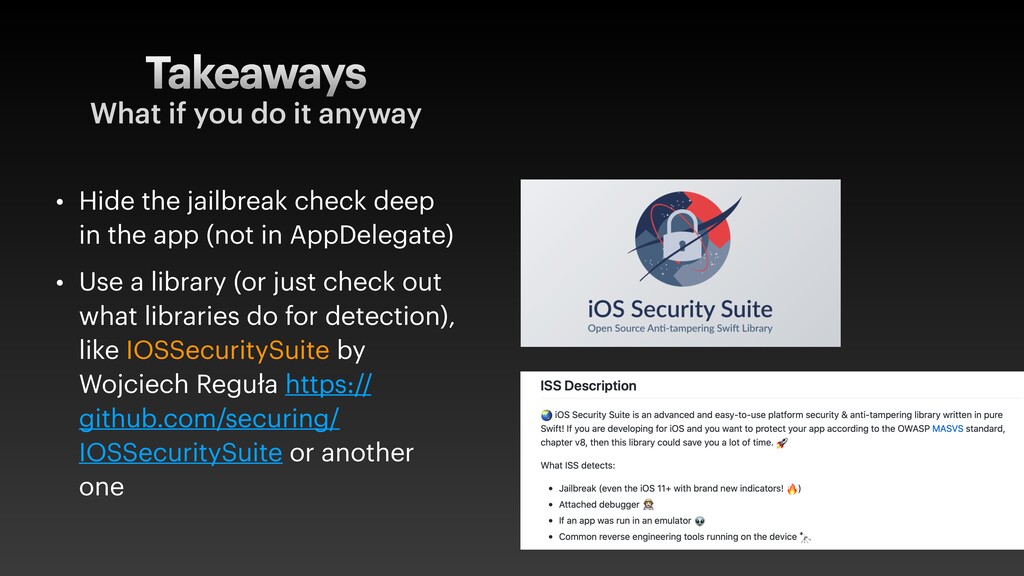
(not in AppDelegate) • Use a library (or just check out what libraries do for detection), like IOSSecuritySuite by Wojciech Reguła https:// github.com/securing/ IOSSecuritySuite or another one What if you do it anyway
display a specific web page by request of other app • You implement a URL scheme handler • Another app registers the same URL scheme (Apple allows it) • Other app pretends to be your app and tricks user to type in the password
to display a specific web page by request of other app • You implement a URL scheme handler, that parses received URL, extracts HTML and opens a web view • Other app passes you a page, that looks exactly like an installed banking app login page. Users type in their credentials. Your app is in the news
to use a 3rd party cloud database, and you get the private key to authenticate • You store it as a string in the codebase • A reverse engineer runs strings command on your binary, acquires the key, steals the data and publishes it in the internet
, authentication details, that you store locally in any way (in a separate file, in codebase, obfuscated or not) • Use acquired credentials to pretend to be your app and use it agains you
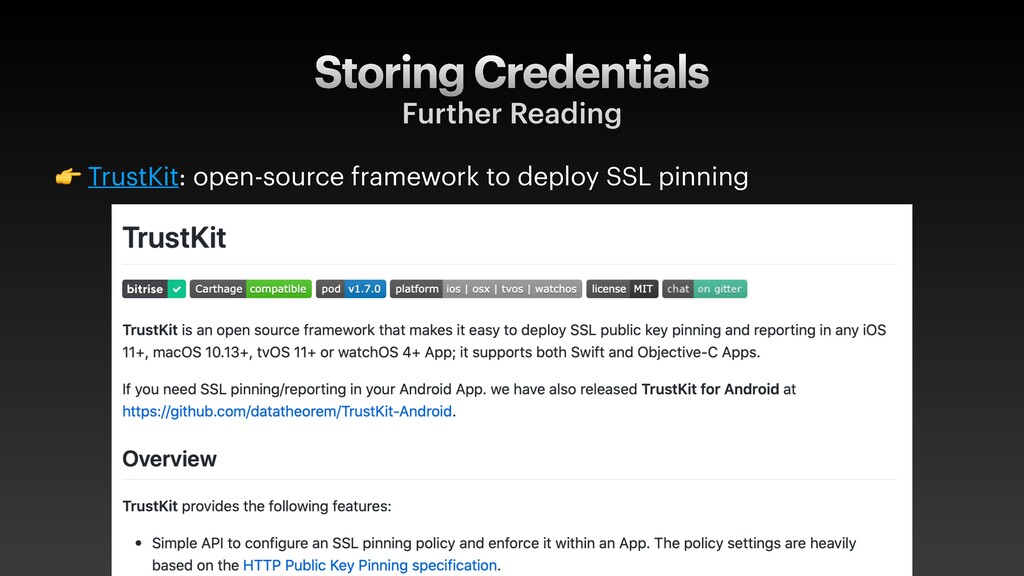
any way. ✓ Store credentials on your remote server, and connect to it instead of connecting to the cloud database directly. Your app must authenticate with your server ✓ Implement SSL pinning to be sure, that the server you are talking is the one you expect (there is no man-in-the-middle)
UI a lot like in another app • You notice a nice popular pod in CocoaPods, that implements it • A researcher finds a security bug in this pod, owners quickly patch it • Before you roll out the update all your users are vulnerable to an attack, that is described in the Internet in great detail
UI a lot like in another app • You notice a nice popular pod in CocoaPods, that implements it • A researcher finds a security bug in this pod, owners quickly patch it • Before you roll out the update all your users are vulnerable to an attack, that is described in the Internet in great detail
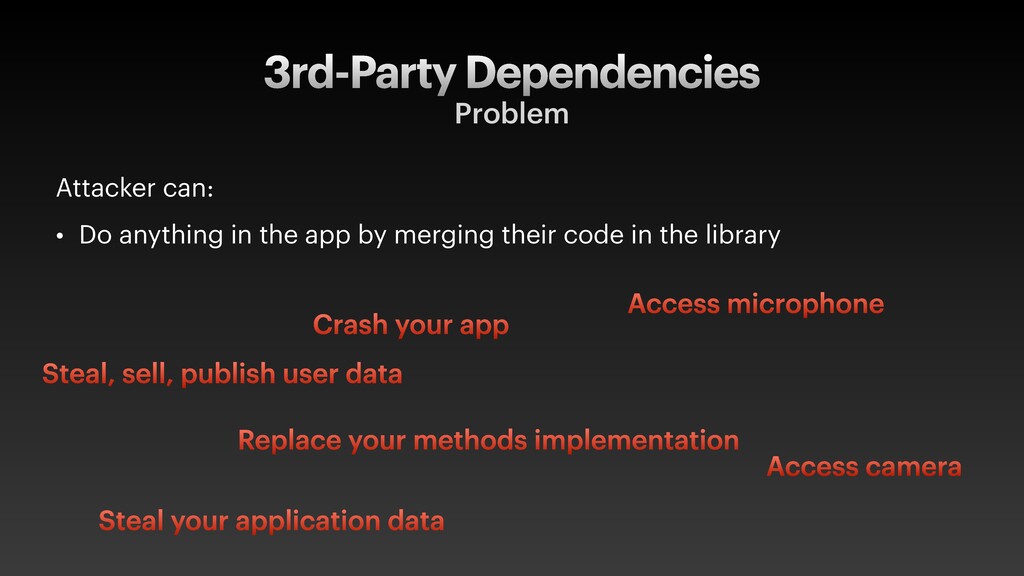
app by merging their code in the library Steal, sell, publish user data Access microphone Access camera Crash your app Steal your application data Replace your methods implementation
mailing list / twitter/ ..., use any channel to get the news about your dependencies (so you know, when there is a security issue) ✓ Minimize the number of dependencies—information on vulnerabilities is fragmented and not easy to track P.S. Dependabot team is working on CocoaPods support
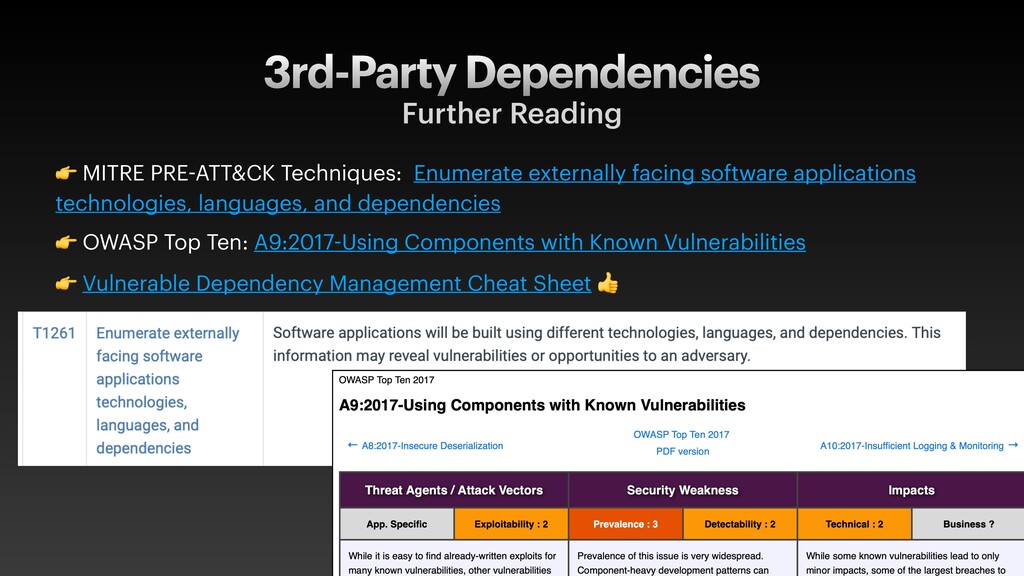
software applications technologies, languages, and dependencies OWASP Top Ten: A9:2017-Using Components with Known Vulnerabilities Vulnerable Dependency Management Cheat Sheet
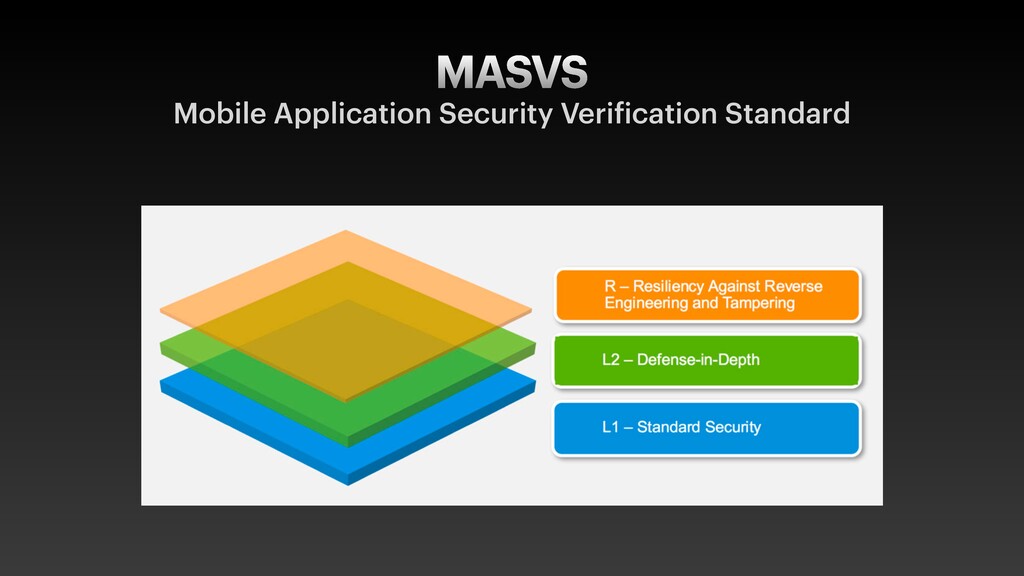
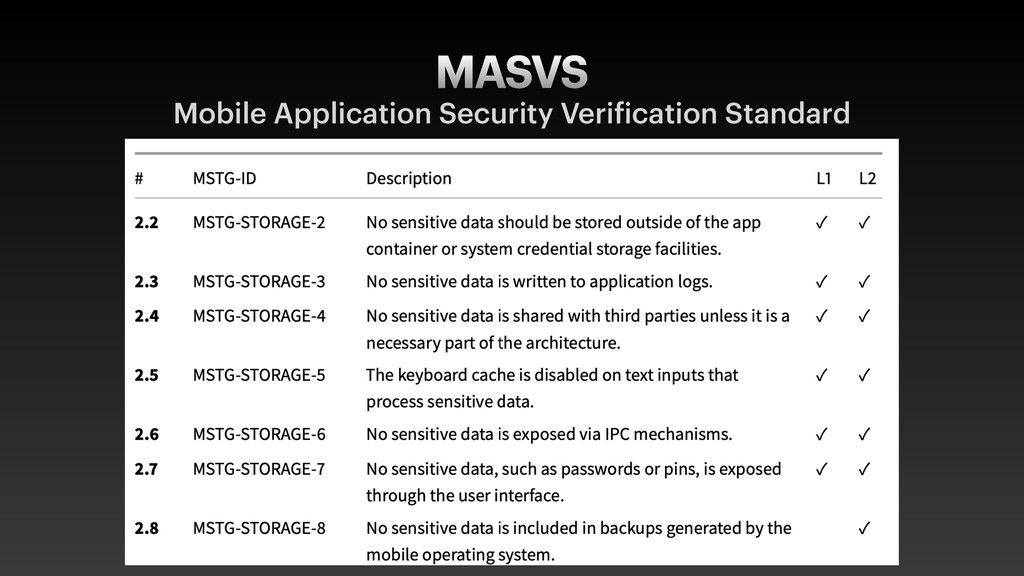
"We don't need any security" • Level 1 + Resilience: Games and Apps, that must protect Intellectual Property • Level 2. Healthcare and Financial • Level 2 + Resilience. On device we need to: protect in-app purchases, store sensitive data, online banking with moving user funds functionality


 vashchenko
 mitohato14
 sobolevn
 dalinaum
 takateeen_knj
 kitano_yuichi
 yasunori0418
 cclai999
 siroemk
 takahirosunaga
 kasacchiful
 t0yohei
 leegeunhyeok
 helenjbeal
 lcolladotor
 geoffreycrofte
 sachag
 schroneko
 honnibal
 marktimemedia
 katarinadahlin
 reverentgeek
 rkaga
 takai