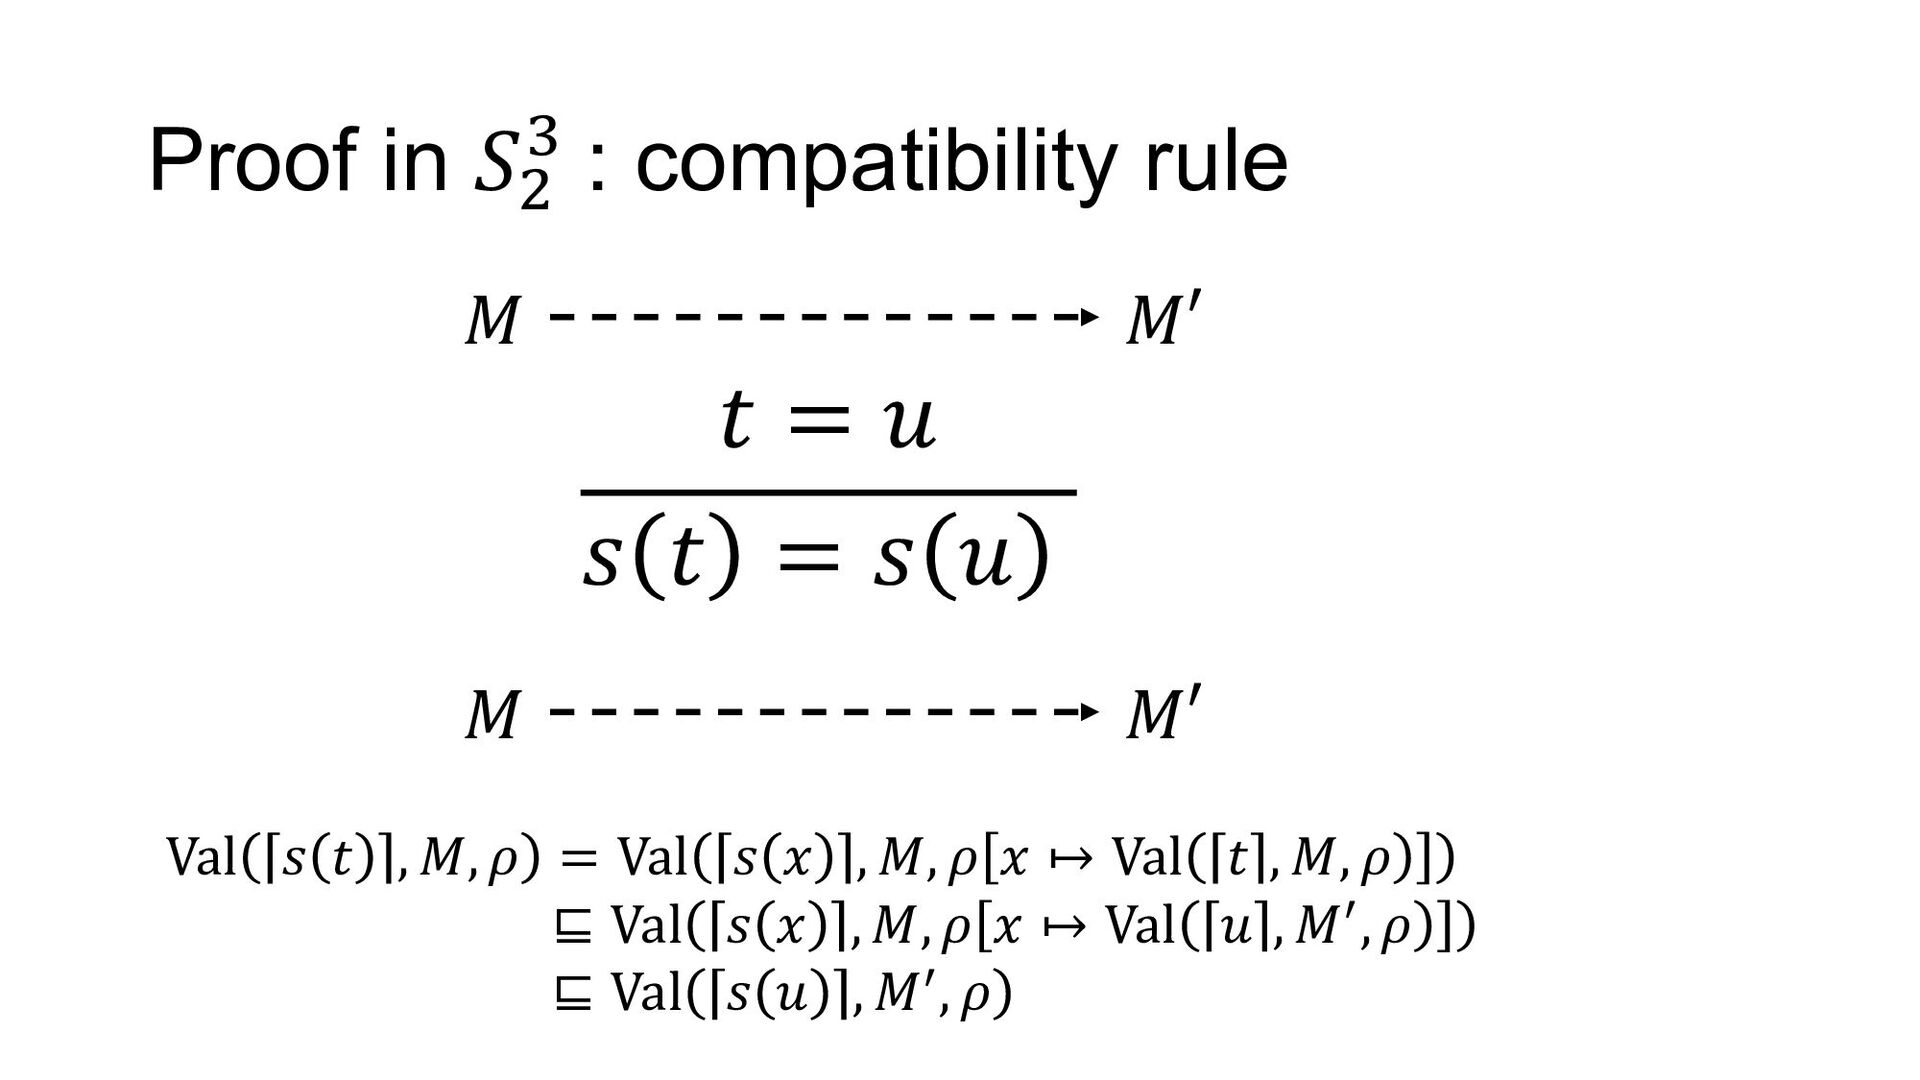Share
Embed
On proving consistency of equational theories in bounded arithmetic
We consider pure equational theories that allow substitution but disallow induction, which we denote as PETS, based on recursive definition of their function symbols. We show that the Bounded Arithmetic theory S12 proves the consistency of PETS. Our approach employs models for PETS based on approximate values resembling notions from domain theory in Bounded Arithmetic, which may be of independent interest.
Yoriyuki Yamagata
May 09, 2022
Transcript
41 slides
-
On proving consistency of equational theories in bounded arithmetic Arnold
Beckmann and Yoriyuki Yamagata Prague logic seminar, 2022-05-09 -
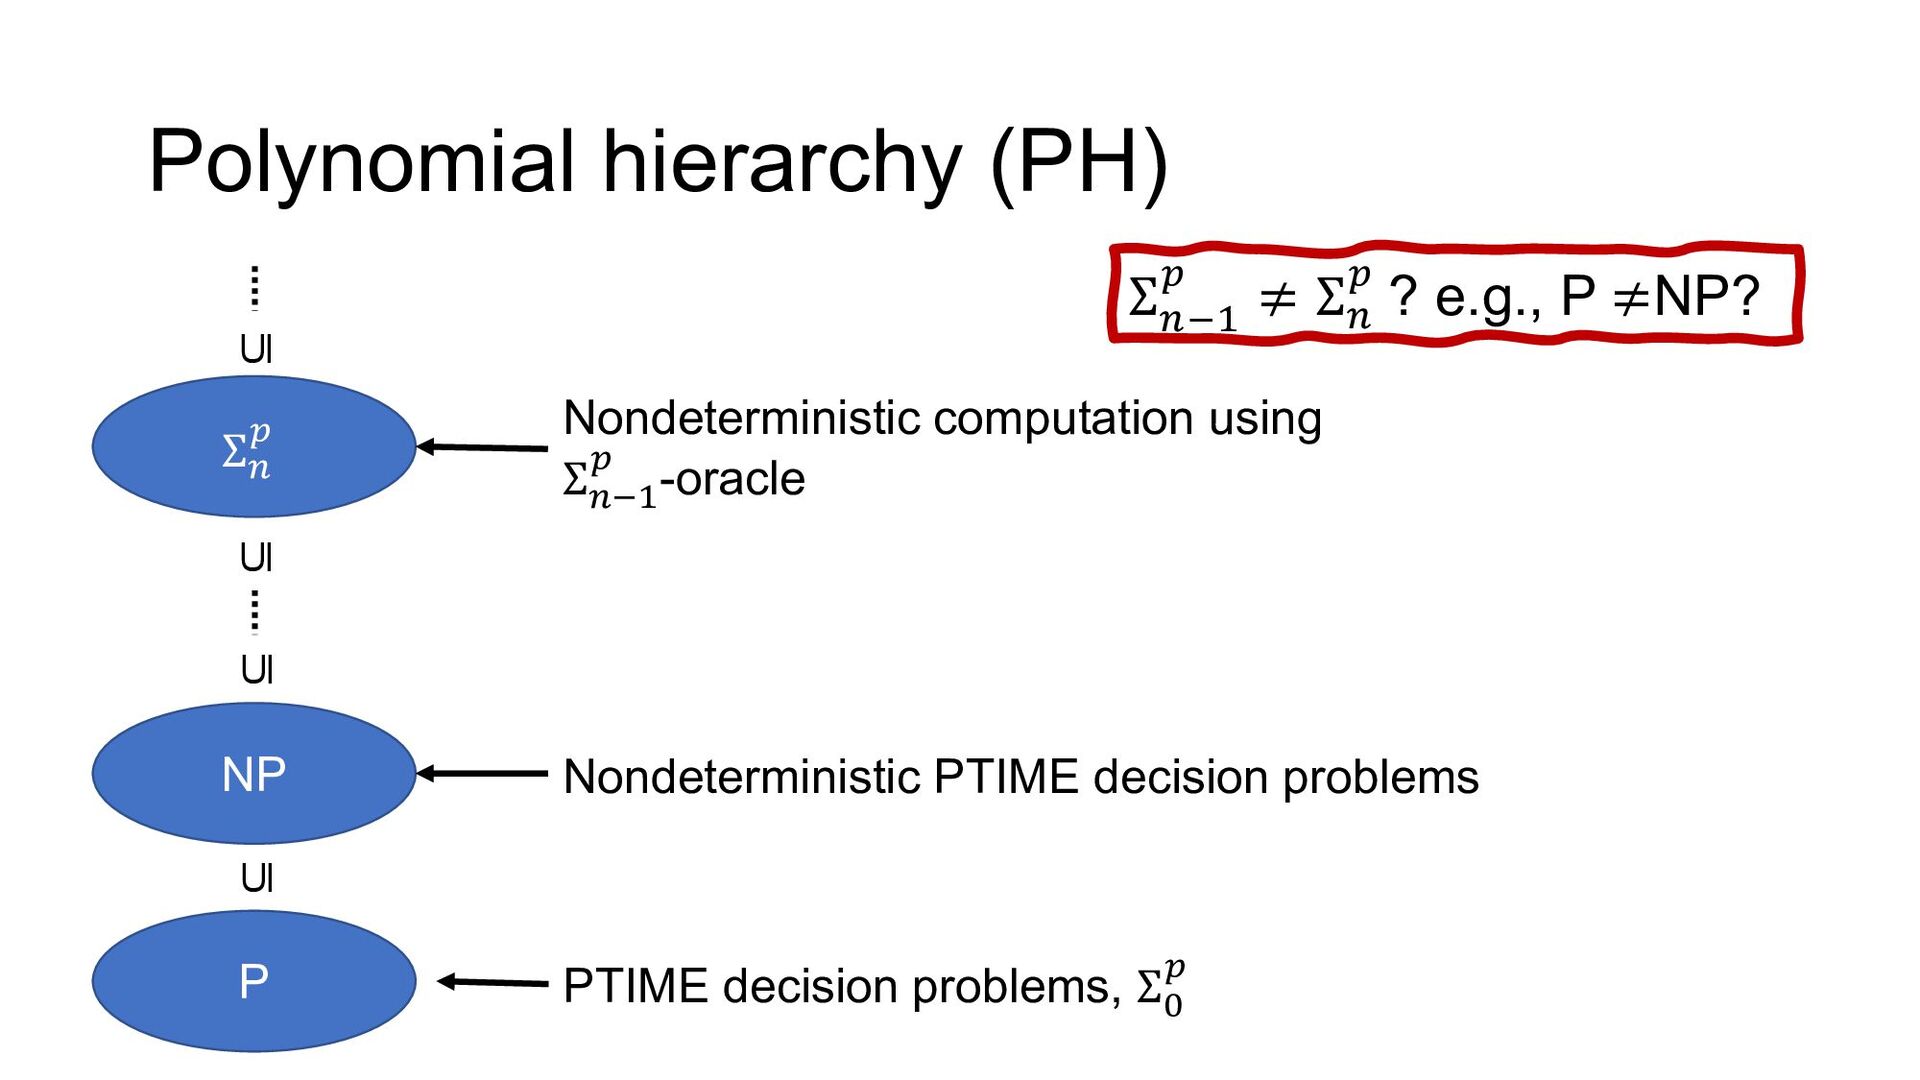
Polynomial hierarchy (PH) P NP Σ! " ⊆ ⊆ ⊆
⊆ PTIME decision problems, Σ# " Nondeterministic PTIME decision problems Nondeterministic computation using Σ!$% " -oracle Σ!"# $ ≠ Σ! $ ? e.g., P ≠NP? -
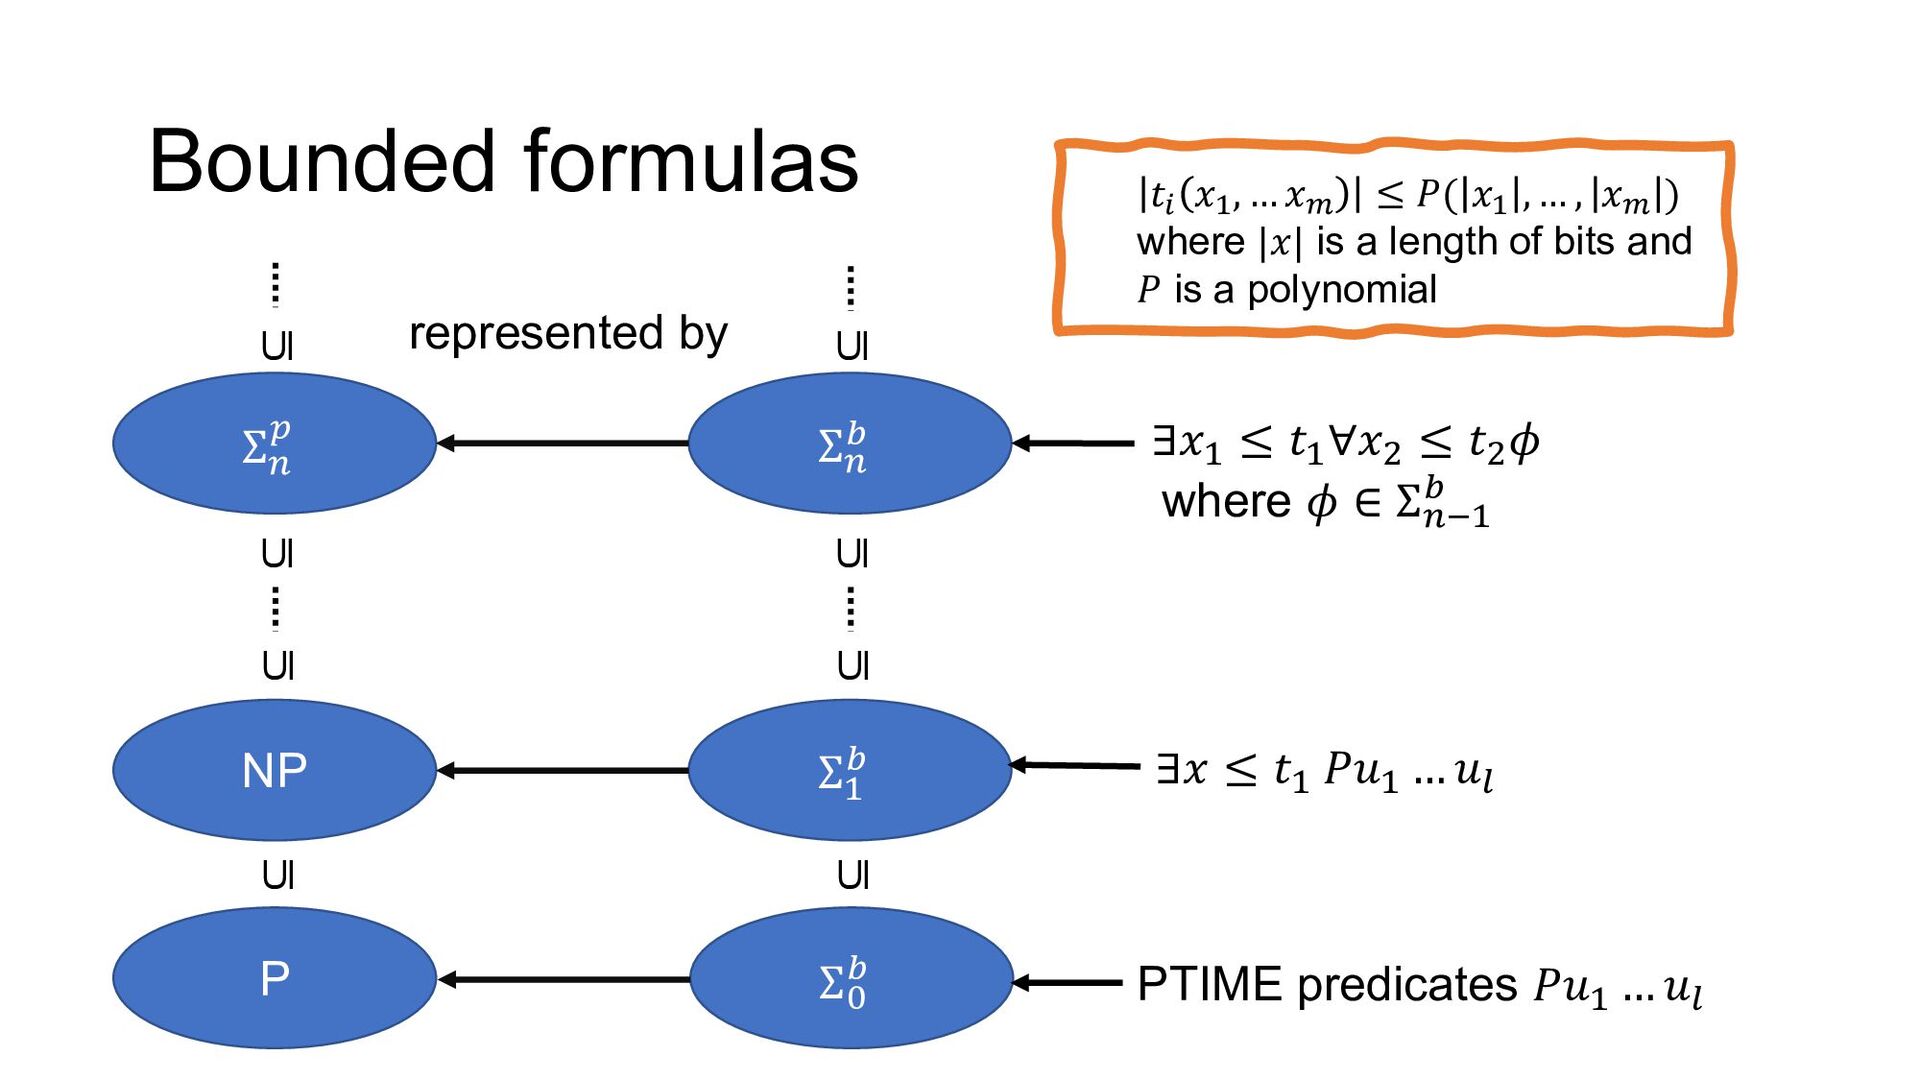
Bounded formulas ∃𝑥% ≤ 𝑡%∀𝑥& ≤ 𝑡&𝜙 where 𝜙 ∈
Σ!$% ' Σ# ' Σ% ' Σ! ' ⊆ ⊆ ⊆ ⊆ PTIME predicates 𝑃𝑢% … 𝑢( ∃𝑥 ≤ 𝑡% 𝑃𝑢% … 𝑢( P NP Σ! " ⊆ ⊆ ⊆ ⊆ represented by 𝑡! 𝑥", … 𝑥# ≤ 𝑃( 𝑥" , … , 𝑥# ) where |𝑥| is a length of bits and 𝑃 is a polynomial -
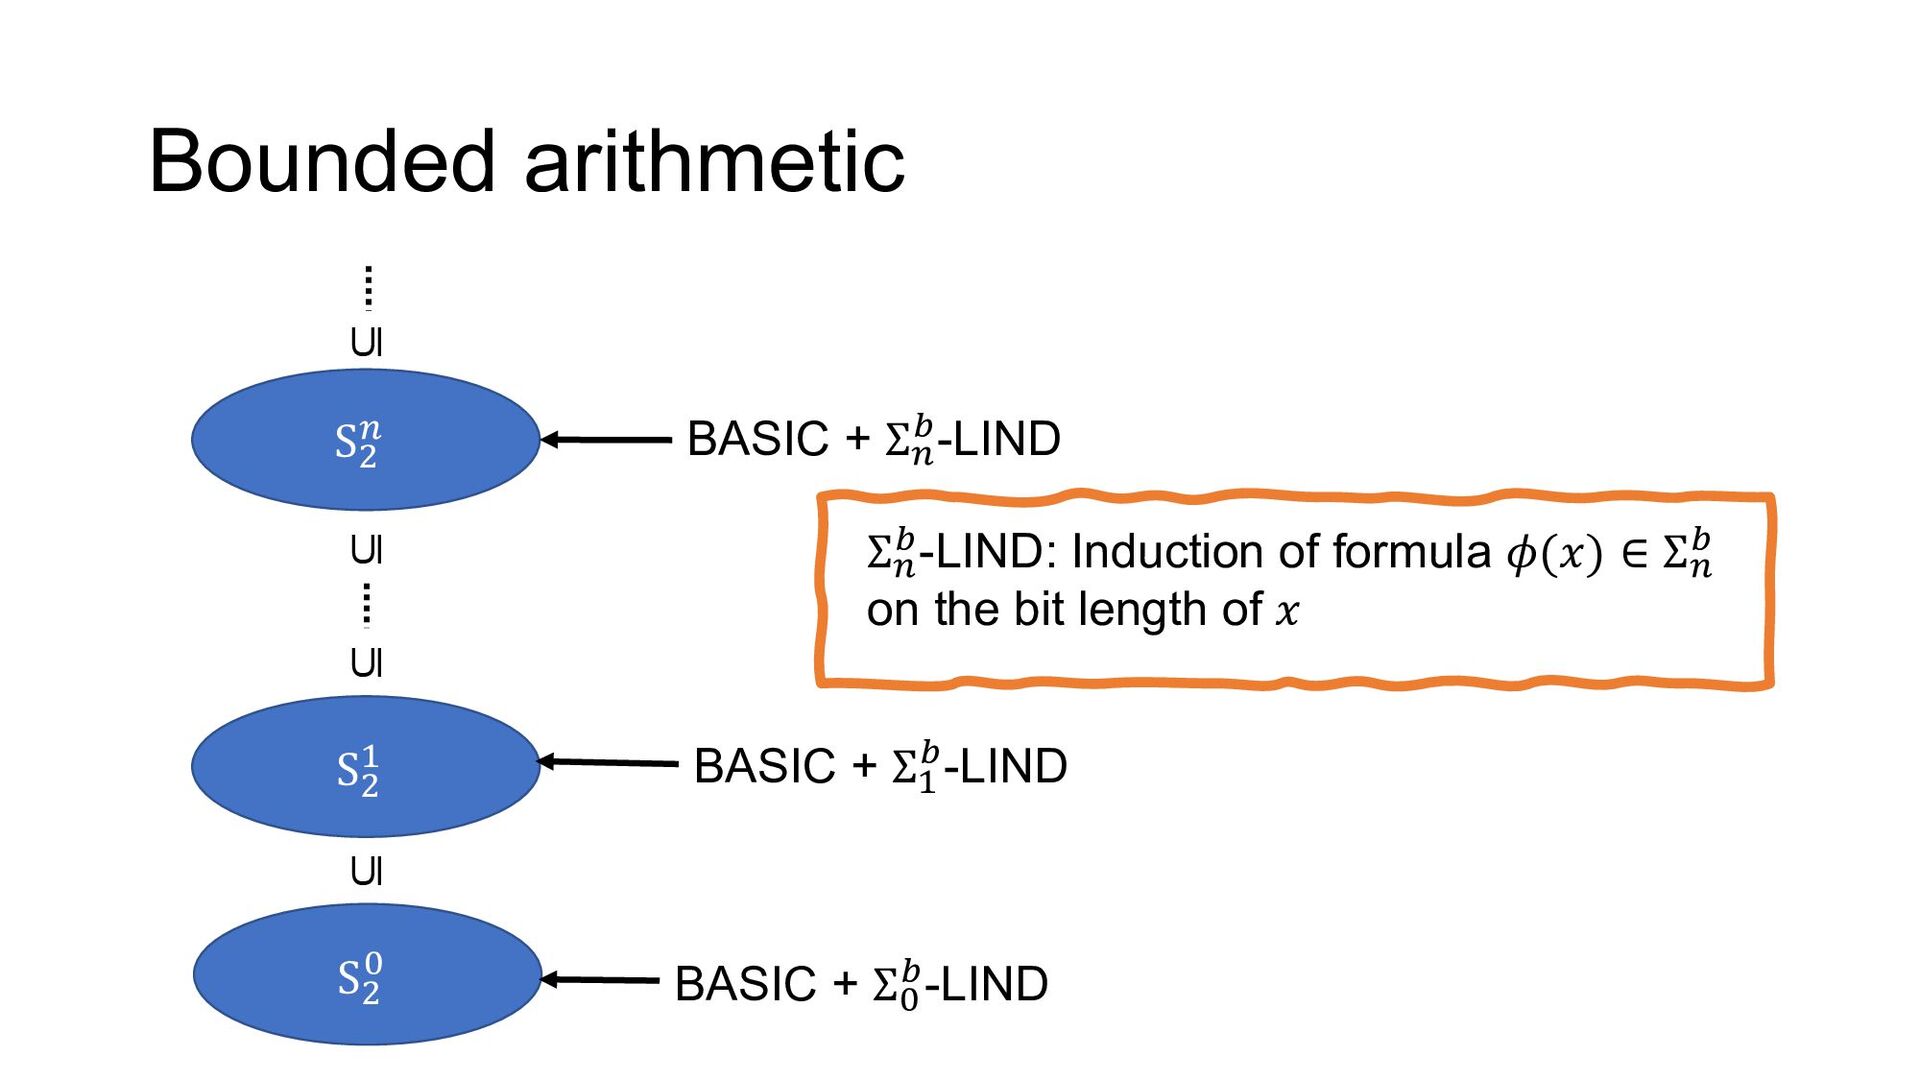
Bounded arithmetic BASIC + Σ! '-LIND S& # S& %
S& ! ⊆ ⊆ ⊆ ⊆ BASIC + Σ# '-LIND BASIC + Σ% '-LIND Σ! '-LIND: Induction of formula 𝜙(𝑥) ∈ Σ! ' on the bit length of 𝑥 -
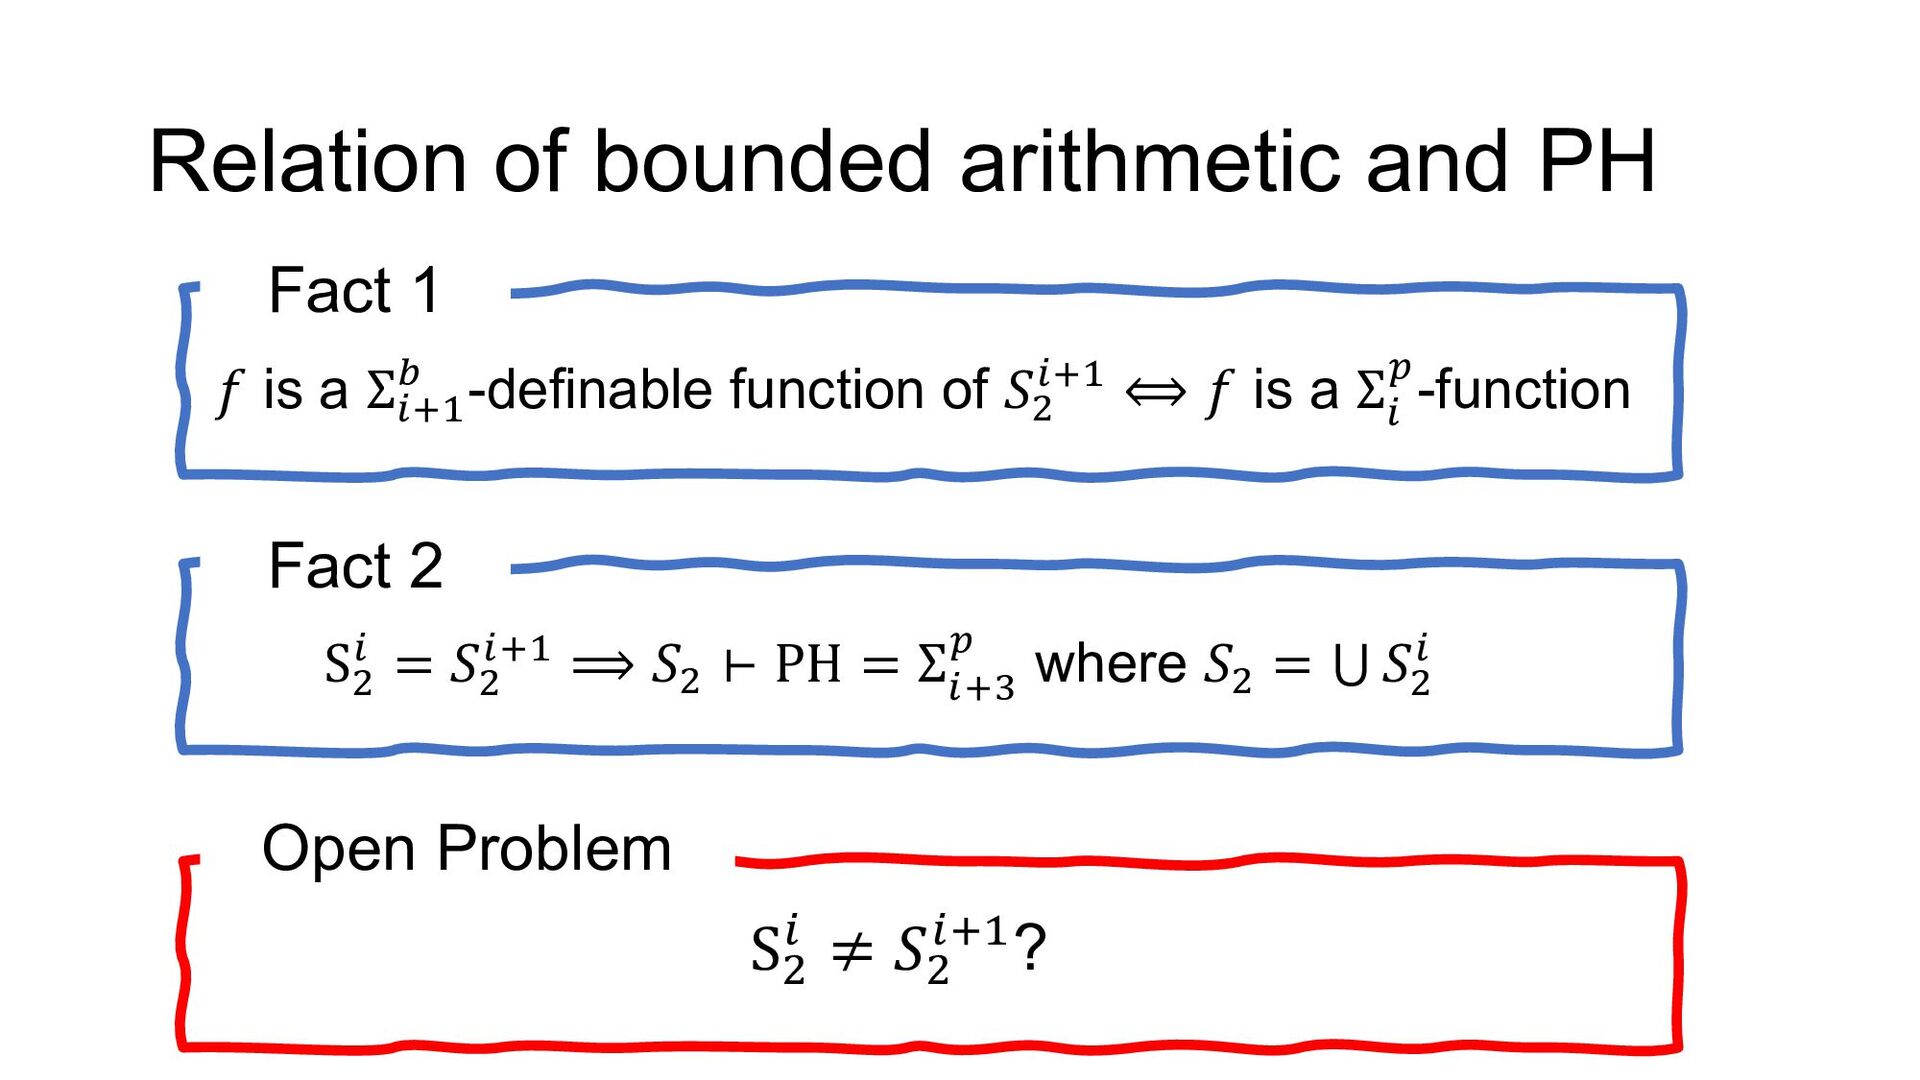
Relation of bounded arithmetic and PH Fact 1 𝑓 is
a Σ./# 0 -definable function of 𝑆1 ./# ⟺ 𝑓 is a Σ. $-function Fact 2 S1 . = 𝑆1 ./# ⟹ 𝑆1 ⊢ PH = Σ ./2 $ where 𝑆1 = ⋃ 𝑆1 . Open Problem S! " ≠ 𝑆! "#$? -
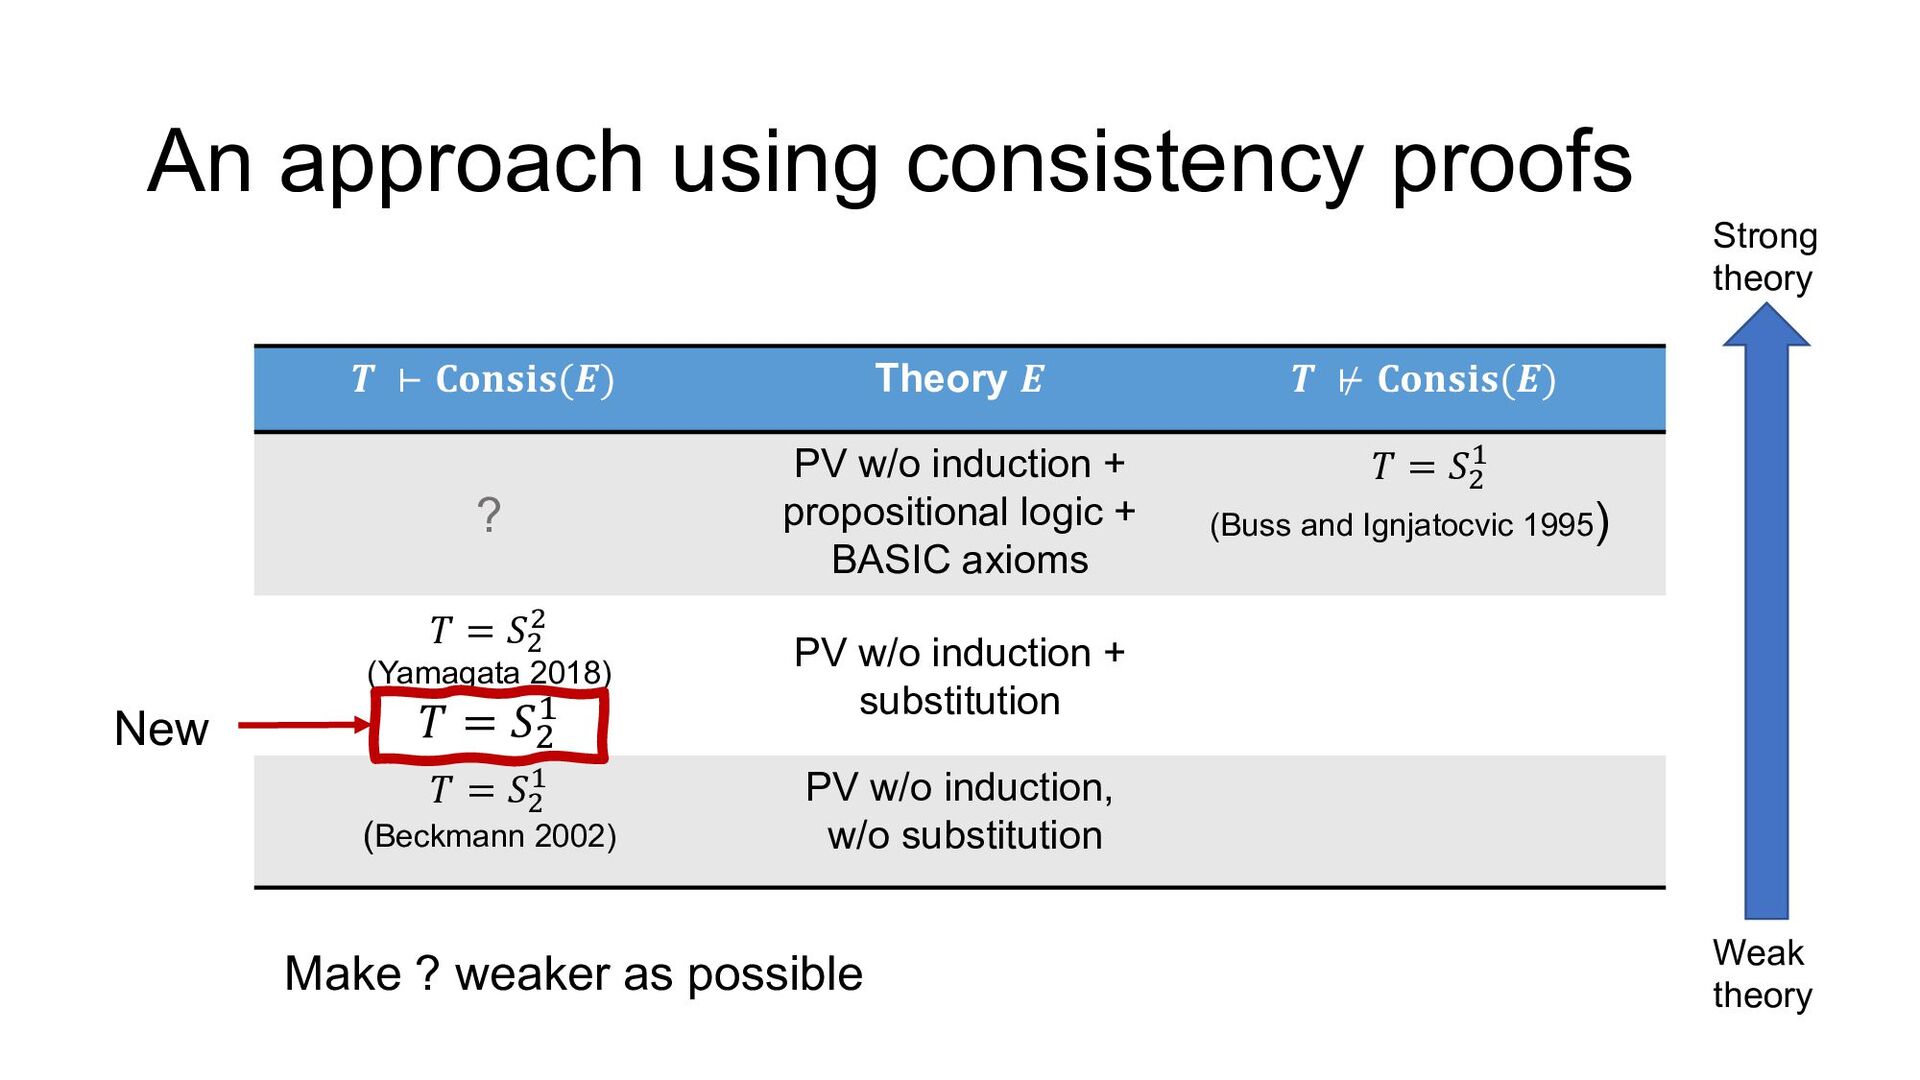
𝑻 ⊢ 𝐂𝐨𝐧𝐬𝐢𝐬(𝑬) Theory 𝑬 𝑻 ⊬ 𝐂𝐨𝐧𝐬𝐢𝐬(𝑬) ? PV
w/o induction + propositional logic + BASIC axioms 𝑇 = 𝑆$ " (Buss and Ignjatocvic 1995) 𝑇 = 𝑆$ $ (Yamagata 2018) 𝑇 = 𝑆& % PV w/o induction + substitution 𝑇 = 𝑆$ " (Beckmann 2002) PV w/o induction, w/o substitution An approach using consistency proofs New Make ? weaker as possible Strong theory Weak theory -
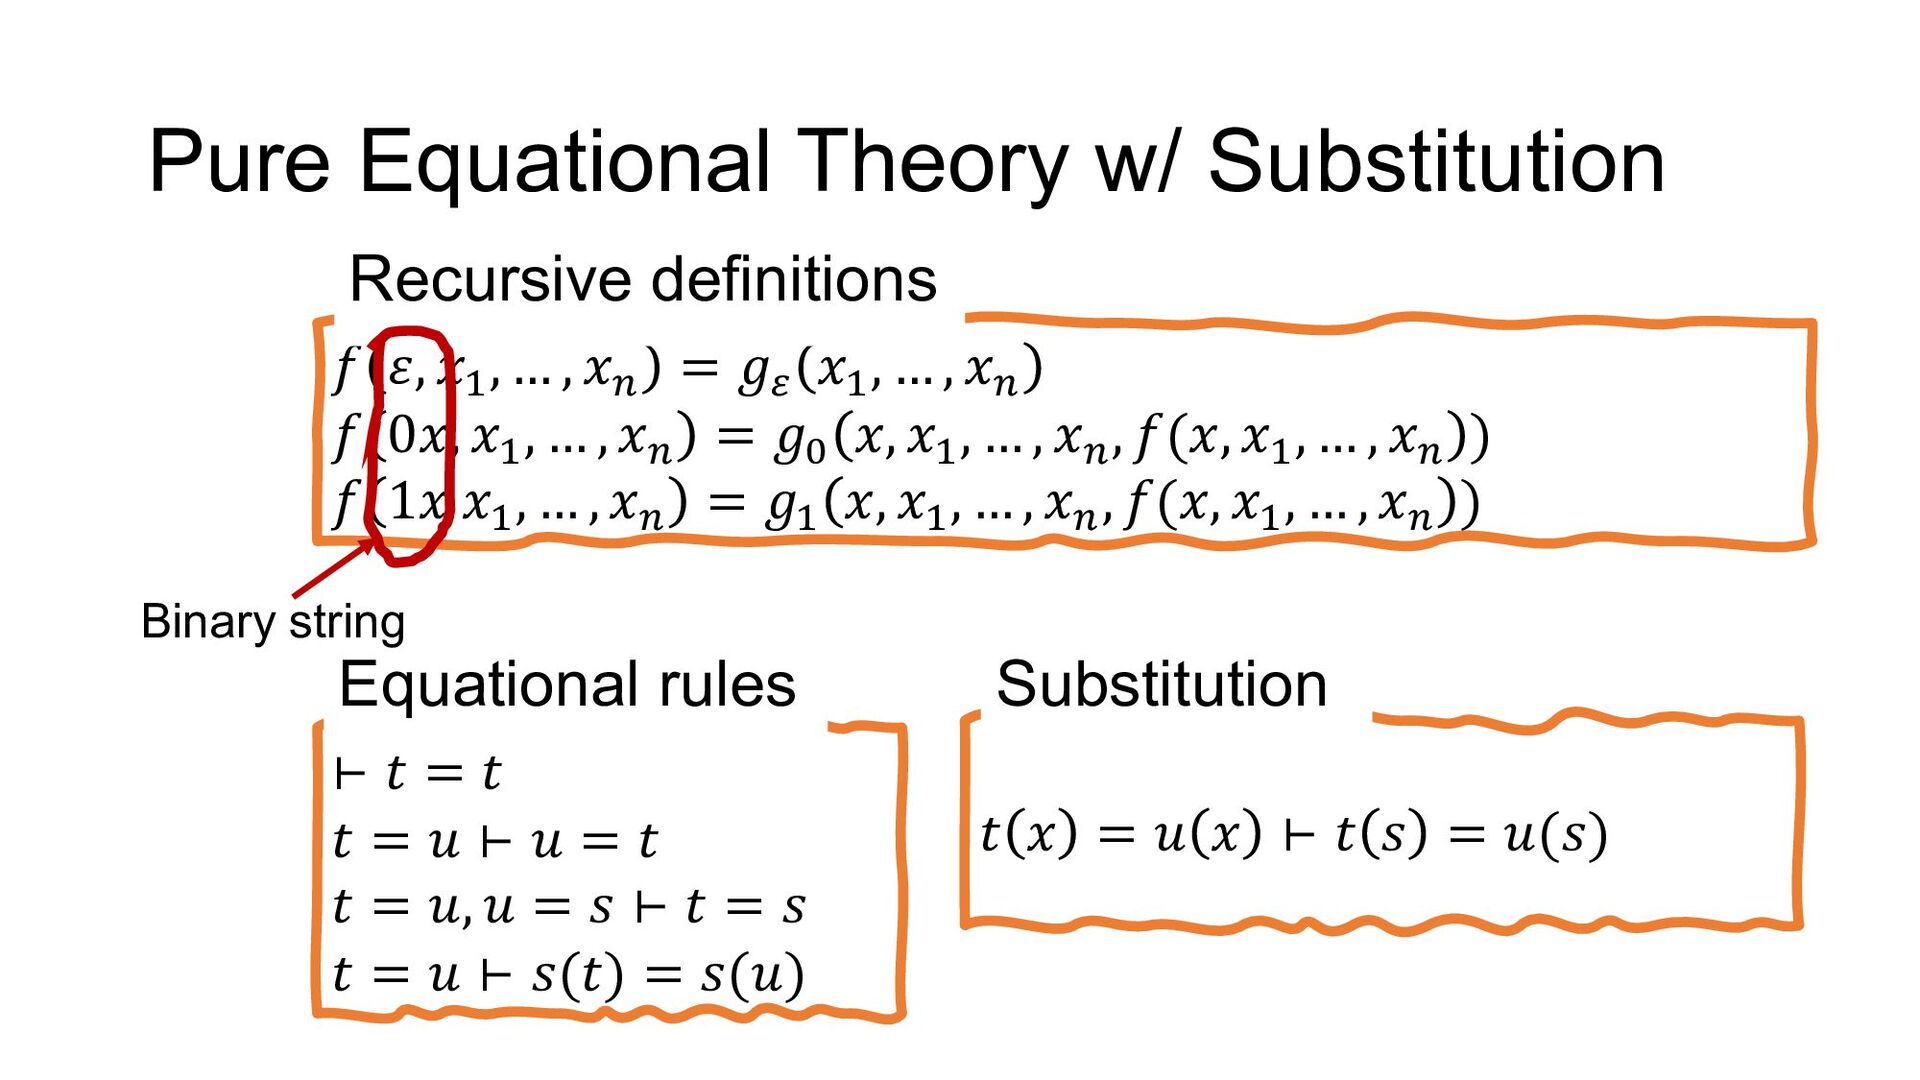
Pure Equational Theory w/ Substitution 𝑓 𝜀, 𝑥# , …
, 𝑥! = 𝑔? 𝑥# , … , 𝑥! 𝑓 0𝑥, 𝑥# , … , 𝑥! = 𝑔@ 𝑥, 𝑥# , … , 𝑥! , 𝑓(𝑥, 𝑥# , … , 𝑥! ) 𝑓 1𝑥 𝑥# , … , 𝑥! = 𝑔# 𝑥, 𝑥# , … , 𝑥! , 𝑓(𝑥, 𝑥# , … , 𝑥! ) Recursive definitions ⊢ 𝑡 = 𝑡 𝑡 = 𝑢 ⊢ 𝑢 = 𝑡 𝑡 = 𝑢, 𝑢 = 𝑠 ⊢ 𝑡 = 𝑠 𝑡 = 𝑢 ⊢ 𝑠(𝑡) = 𝑠(𝑢) Equational rules 𝑡 𝑥 = 𝑢 𝑥 ⊢ 𝑡 𝑠 = 𝑢(𝑠) Substitution Binary string -
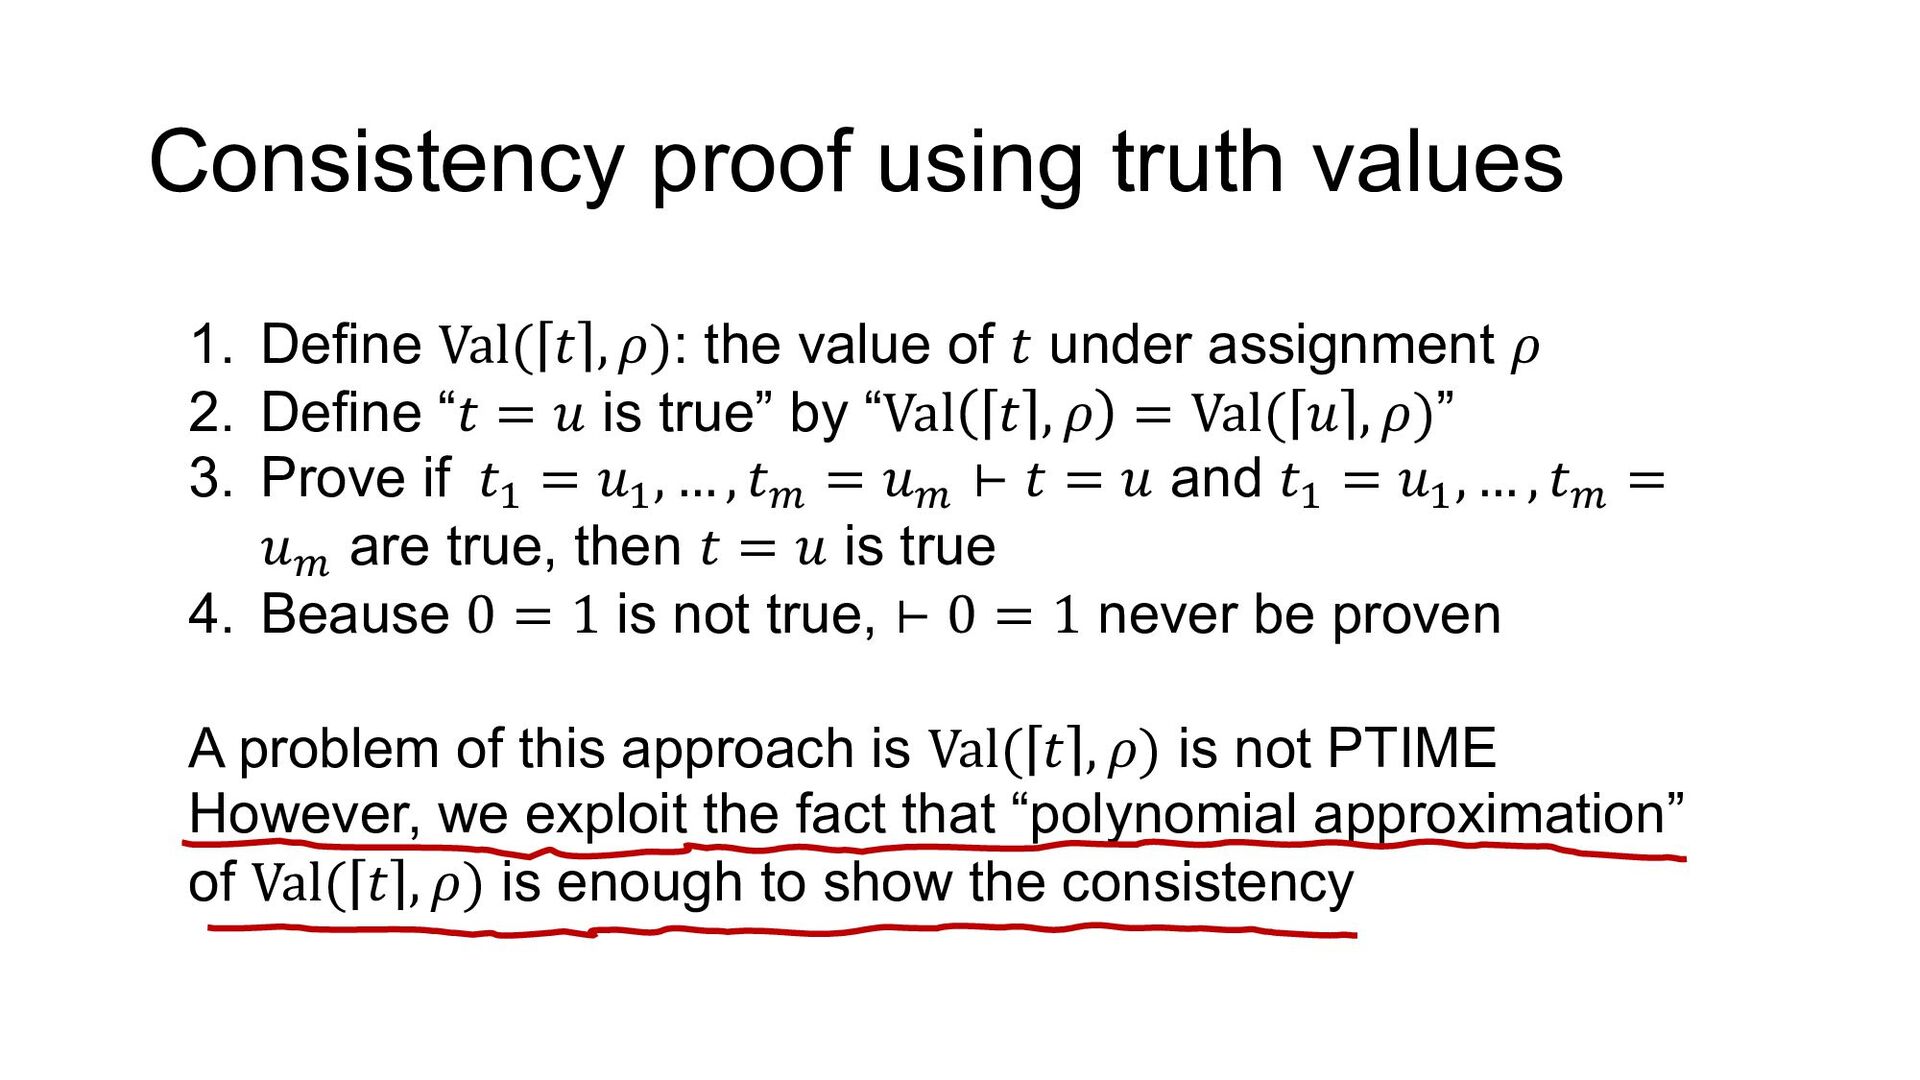
Consistency proof using truth values 1. Define Val( 𝑡 ,
𝜌): the value of 𝑡 under assignment 𝜌 2. Define “𝑡 = 𝑢 is true” by “Val 𝑡 , 𝜌 = Val( 𝑢 , 𝜌)” 3. Prove if 𝑡# = 𝑢# , … , 𝑡A = 𝑢A ⊢ 𝑡 = 𝑢 and 𝑡# = 𝑢# , … , 𝑡A = 𝑢A are true, then 𝑡 = 𝑢 is true 4. Beause 0 = 1 is not true, ⊢ 0 = 1 never be proven A problem of this approach is Val( 𝑡 , 𝜌) is not PTIME However, we exploit the fact that “polynomial approximation” of Val( 𝑡 , 𝜌) is enough to show the consistency -
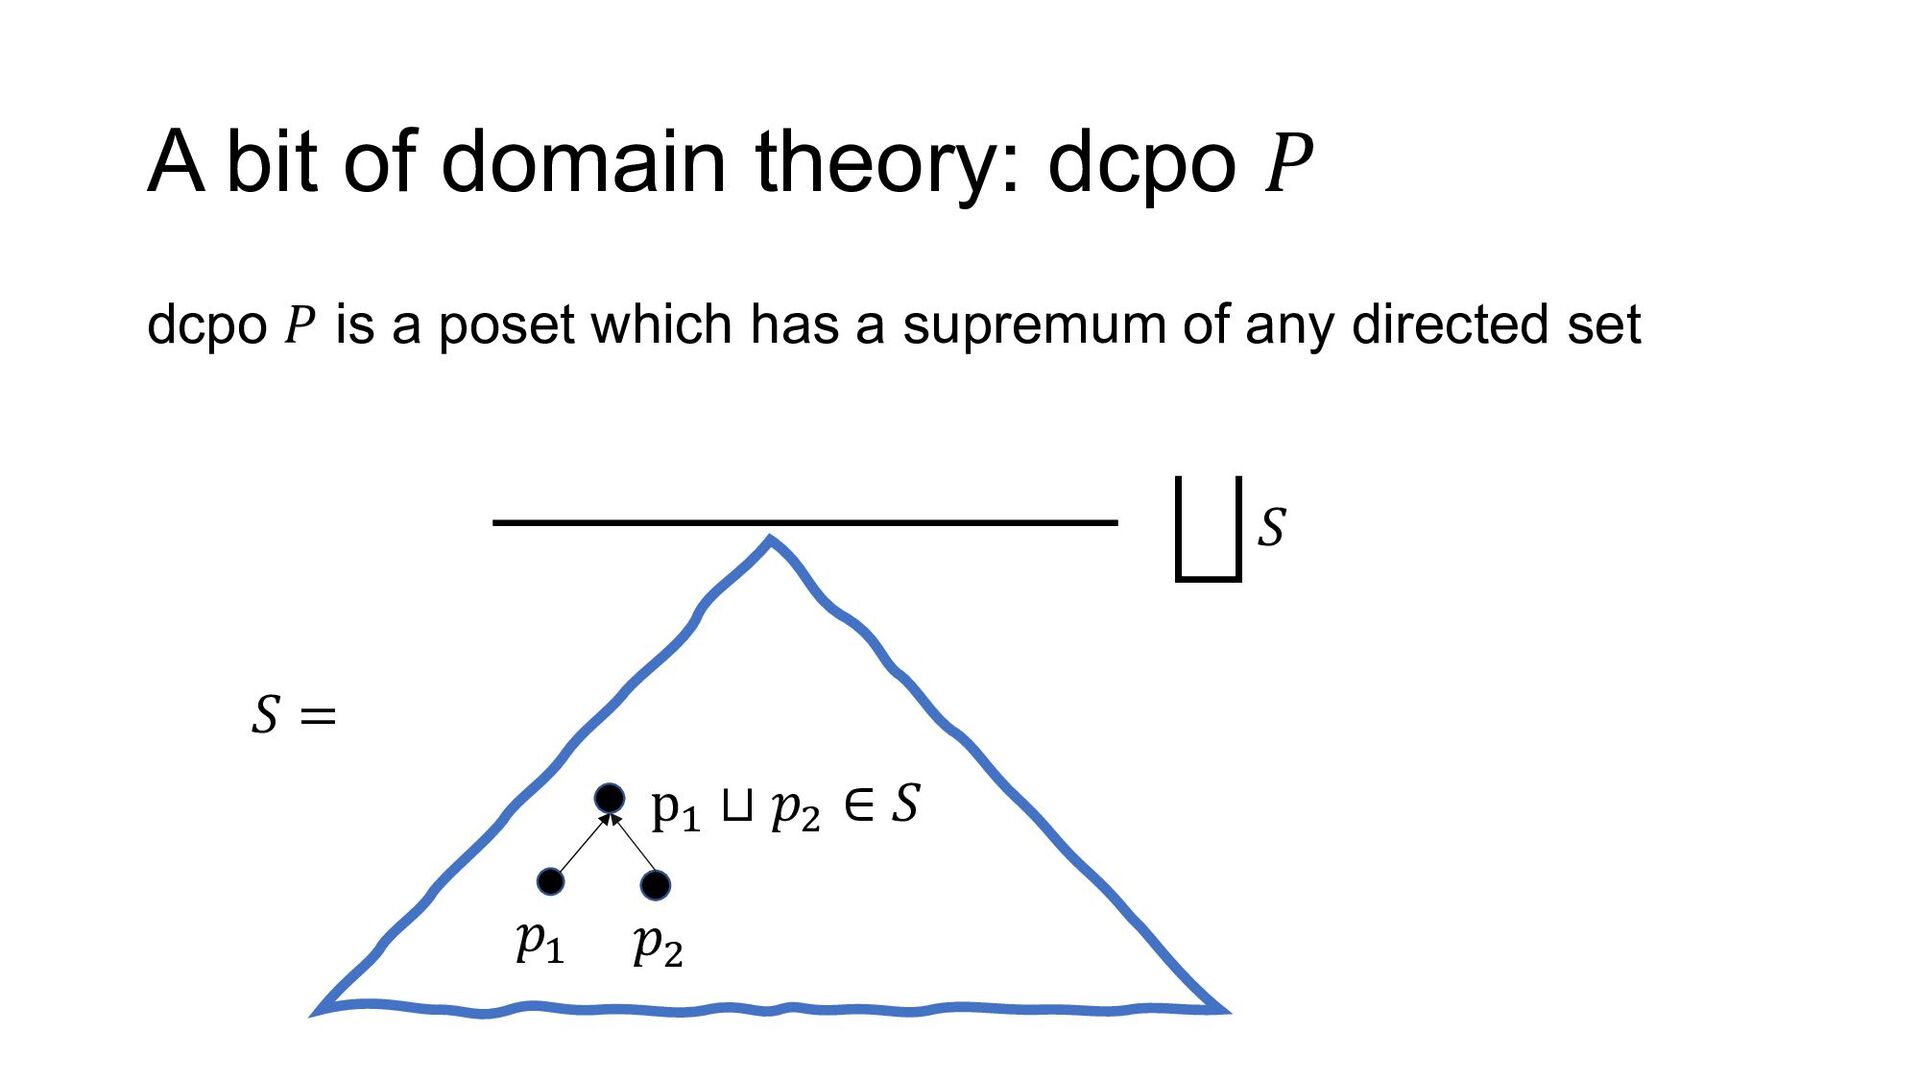
A bit of domain theory: dcpo 𝑃 dcpo 𝑃 is
a poset which has a supremum of any directed set 𝑝# 𝑝1 𝑆 = p# ⊔ 𝑝1 ∈ 𝑆 B 𝑆 -
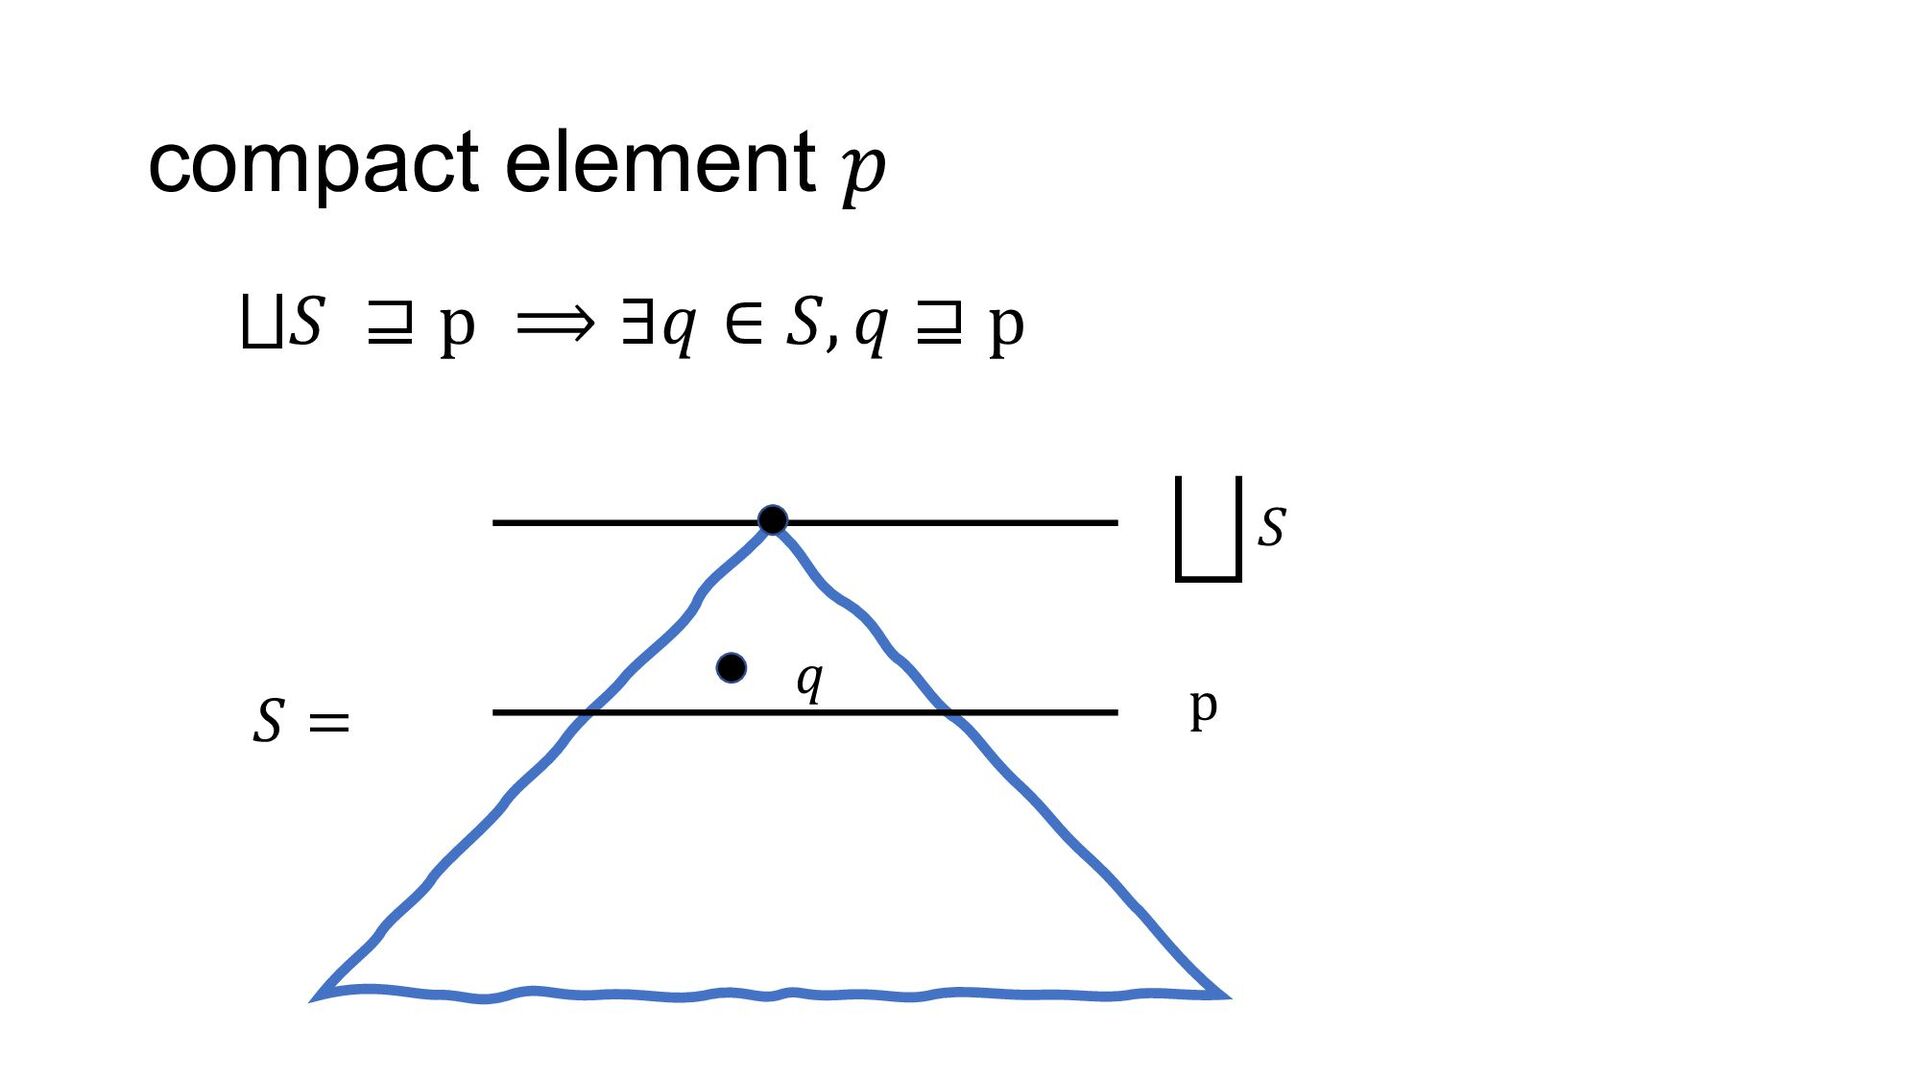
compact element 𝑝 ⨆𝑆 ⊒ p ⟹ ∃𝑞 ∈ 𝑆,
𝑞 ⊒ p 𝑞 𝑆 = B 𝑆 p -
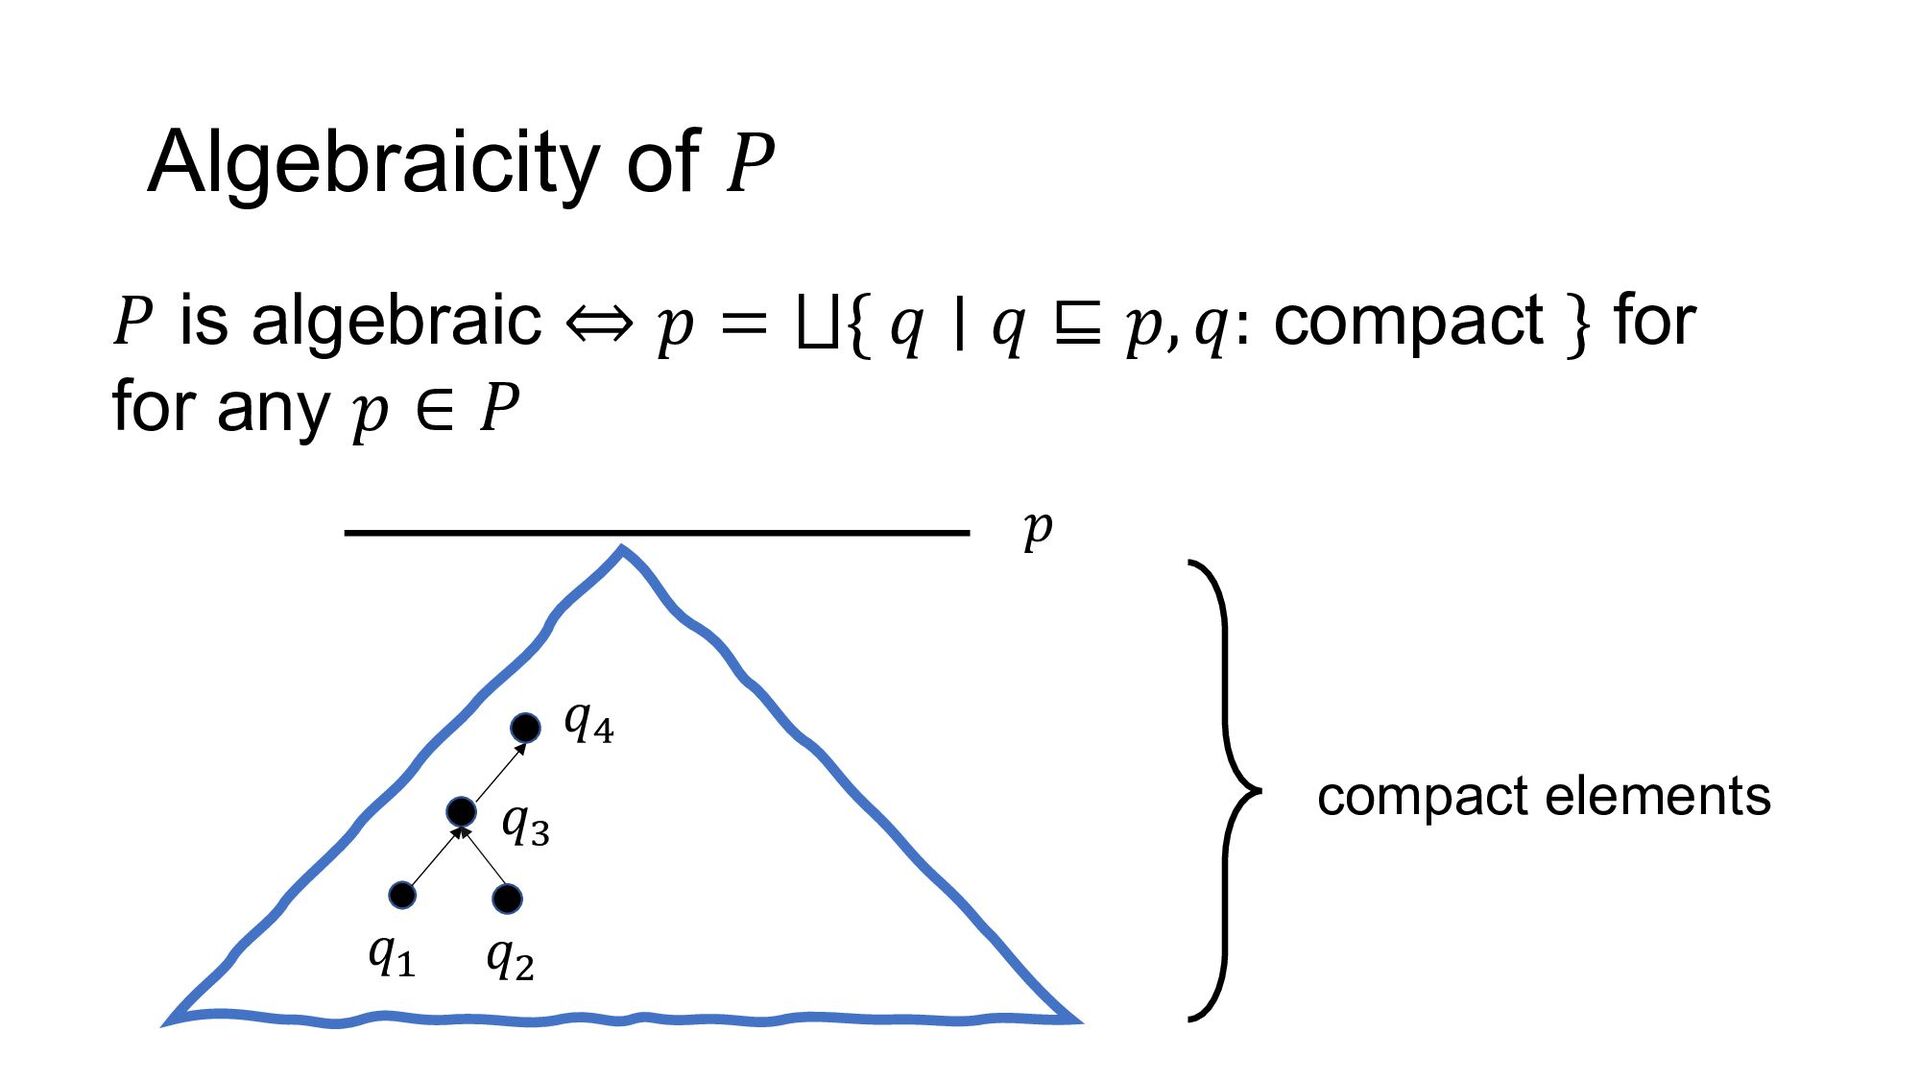
Algebraicity of 𝑃 𝑃 is algebraic ⇔ 𝑝 = ⨆{
𝑞 ∣ 𝑞 ⊑ 𝑝, 𝑞: compact } for for any 𝑝 ∈ 𝑃 𝑝 𝑞# 𝑞1 𝑞2 𝑞B compact elements -
Scott domain Nonempty poset 𝑃 is called “Scott domain” if
•𝑃 is a dcpo •𝑃 is bounded complete, i.e., all bounded subsets have a supremum • 𝑃 is algebraic -
Function space as Scott domain 𝑓: 𝑃 → 𝑄 is
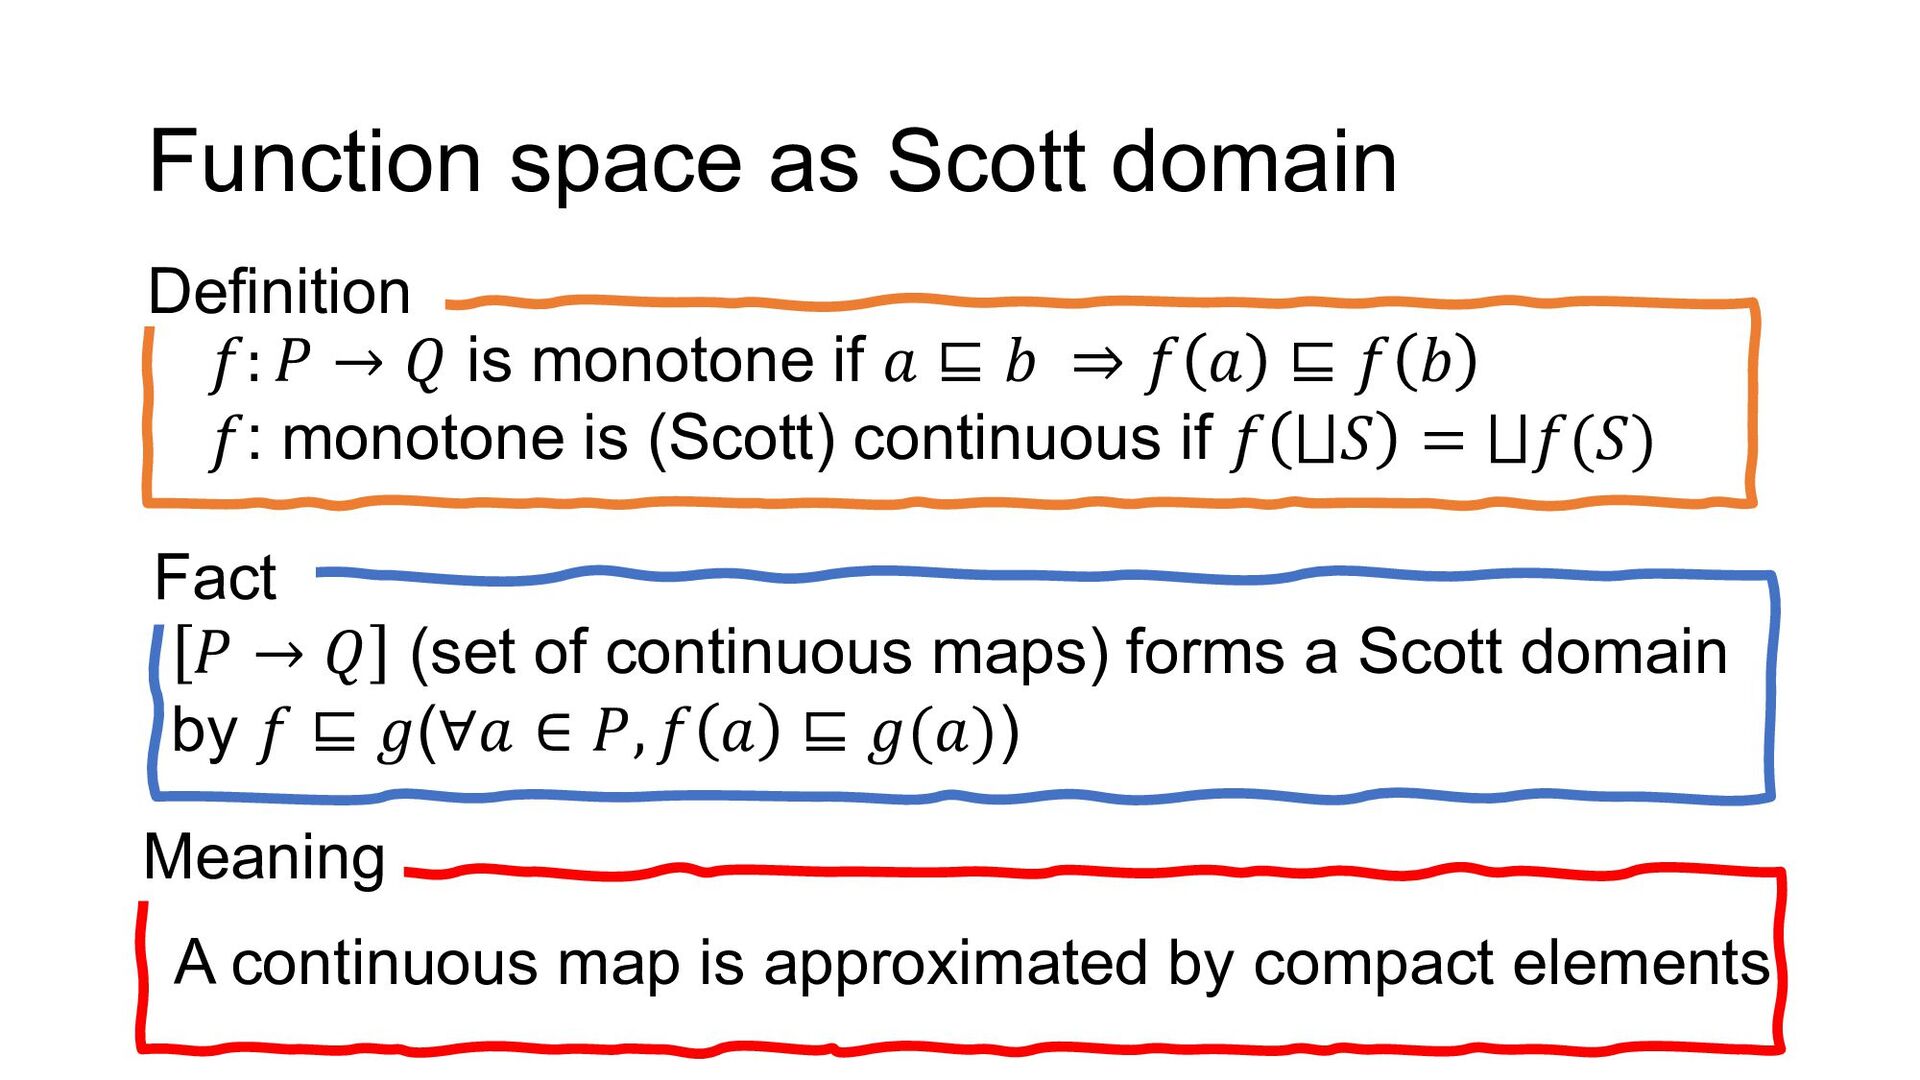
monotone if 𝑎 ⊑ 𝑏 ⇒ 𝑓 𝑎 ⊑ 𝑓 𝑏 𝑓: monotone is (Scott) continuous if 𝑓 ⨆𝑆 = ⨆𝑓(𝑆) Definition Fact 𝑃 → 𝑄 (set of continuous maps) forms a Scott domain by 𝑓 ⊑ 𝑔(∀𝑎 ∈ 𝑃, 𝑓 𝑎 ⊑ 𝑔(𝑎)) A continuous map is approximated by compact elements Meaning -
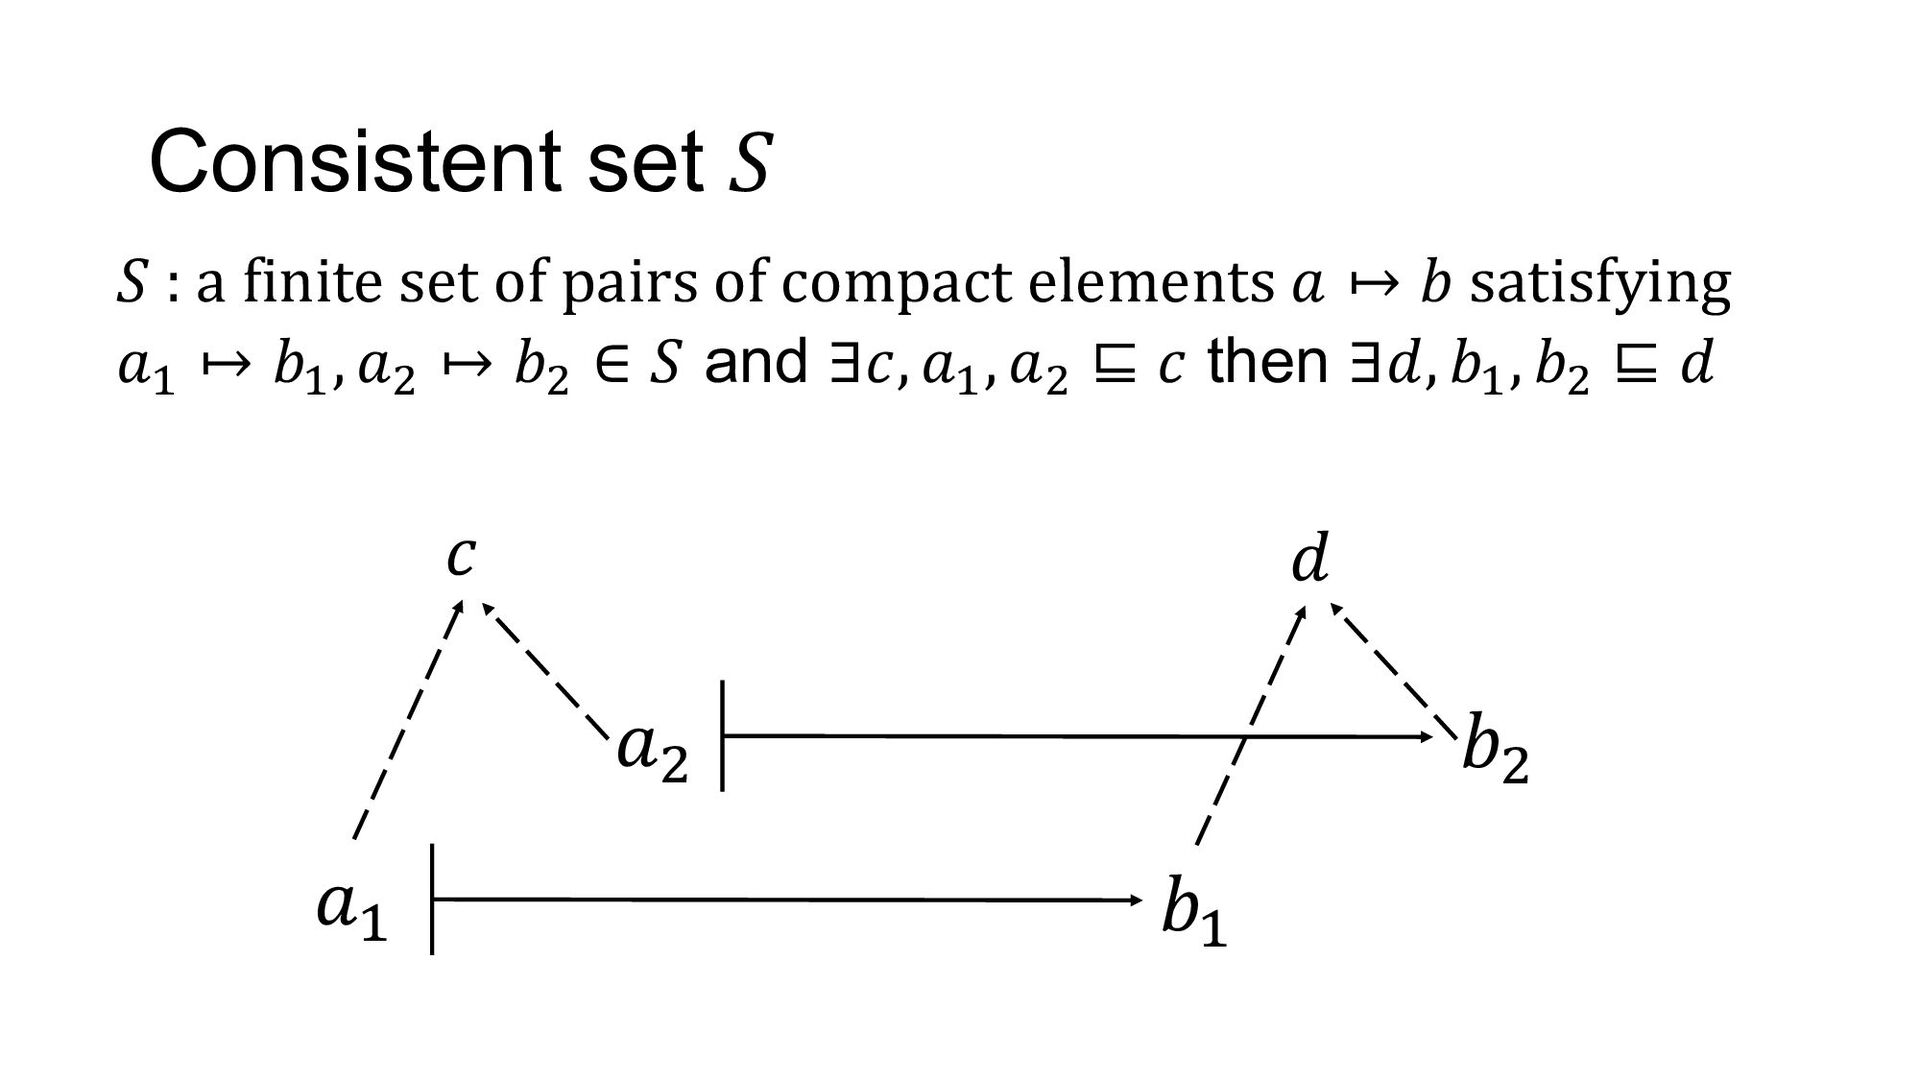
Consistent set 𝑆 𝑆 : a finite set of pairs
of compact elements 𝑎 ↦ 𝑏 satisfying 𝑎$ ↦ 𝑏$ , 𝑎! ↦ 𝑏! ∈ 𝑆 and ∃𝑐, 𝑎$ , 𝑎! ⊑ 𝑐 then ∃𝑑, 𝑏$ , 𝑏! ⊑ 𝑑 𝑎! 𝑎" 𝑐 𝑏! 𝑏" 𝑑 -
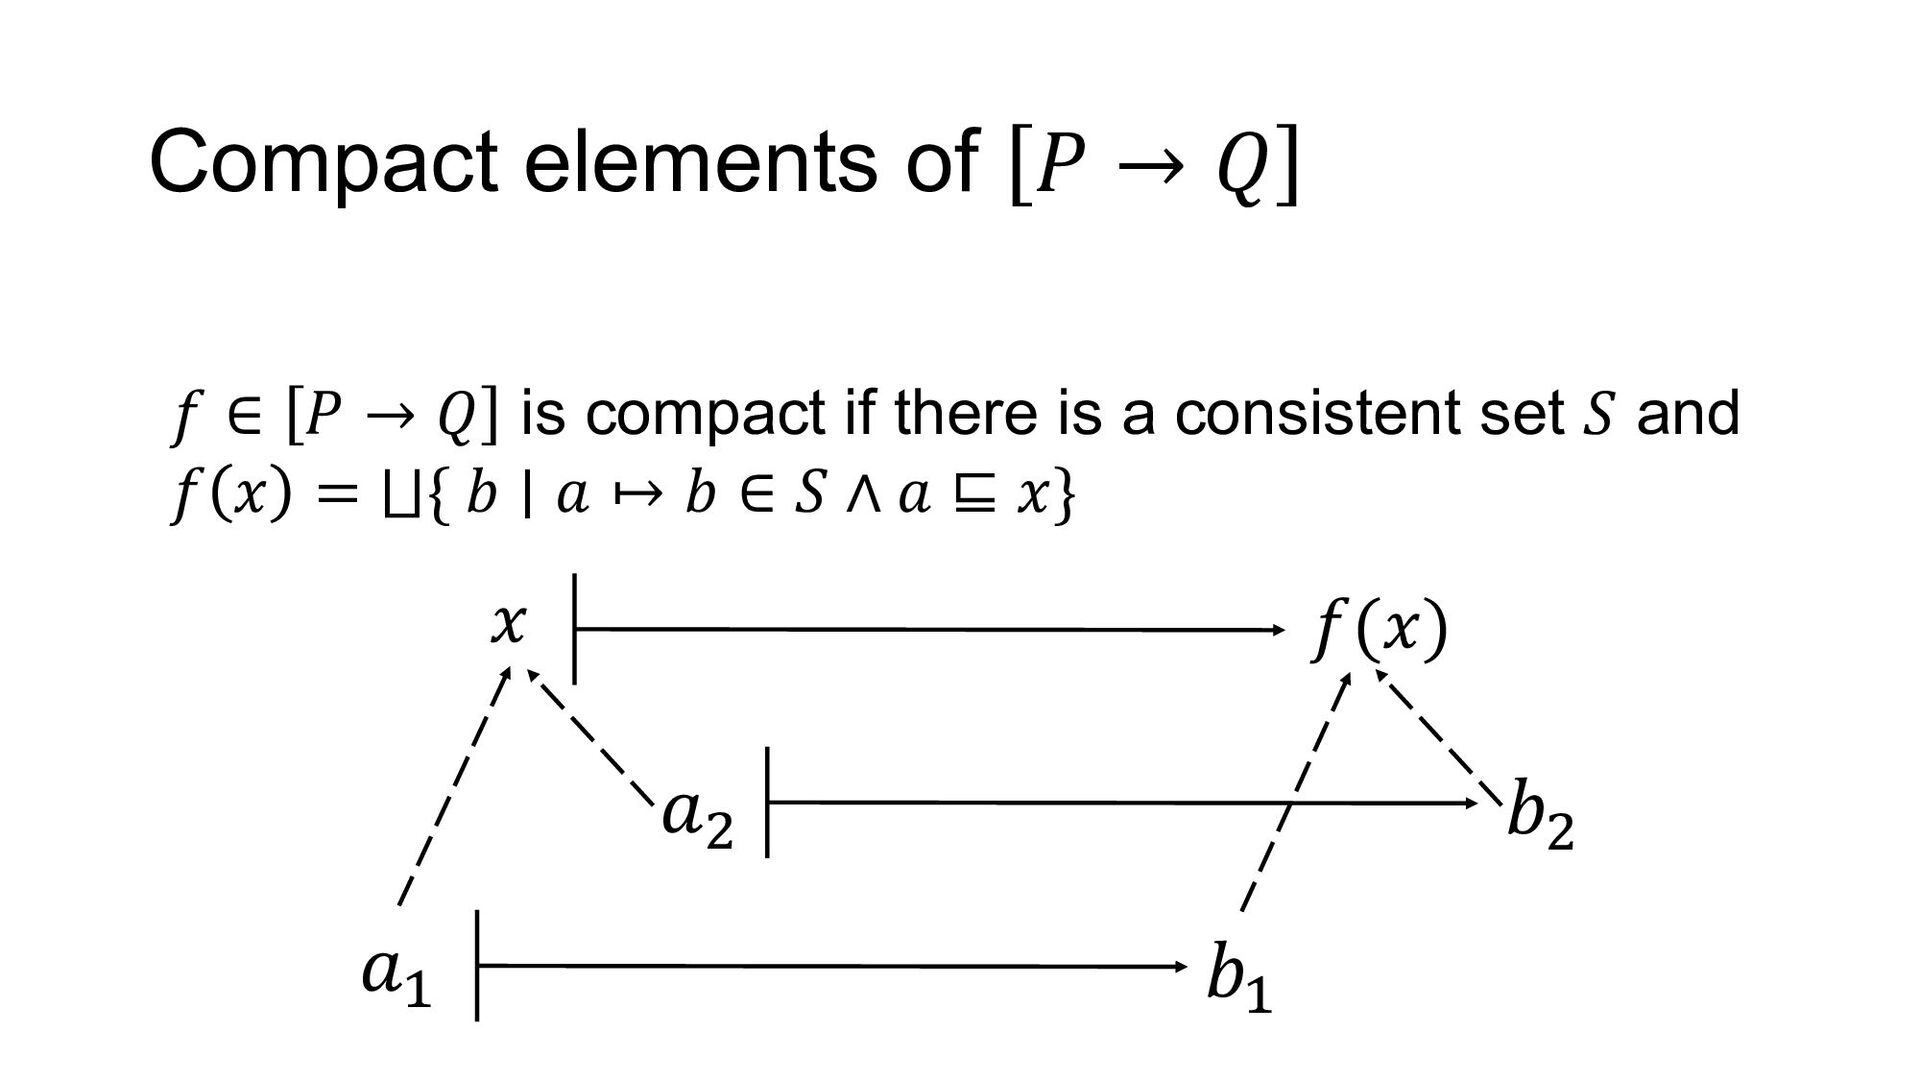
Compact elements of 𝑃 → 𝑄 𝑓 ∈ 𝑃 →
𝑄 is compact if there is a consistent set 𝑆 and 𝑓 𝑥 = ⨆{ 𝑏 ∣ 𝑎 ↦ 𝑏 ∈ 𝑆 ∧ 𝑎 ⊑ 𝑥} 𝑎! 𝑎" 𝑥 𝑏! 𝑏" 𝑓(𝑥) -
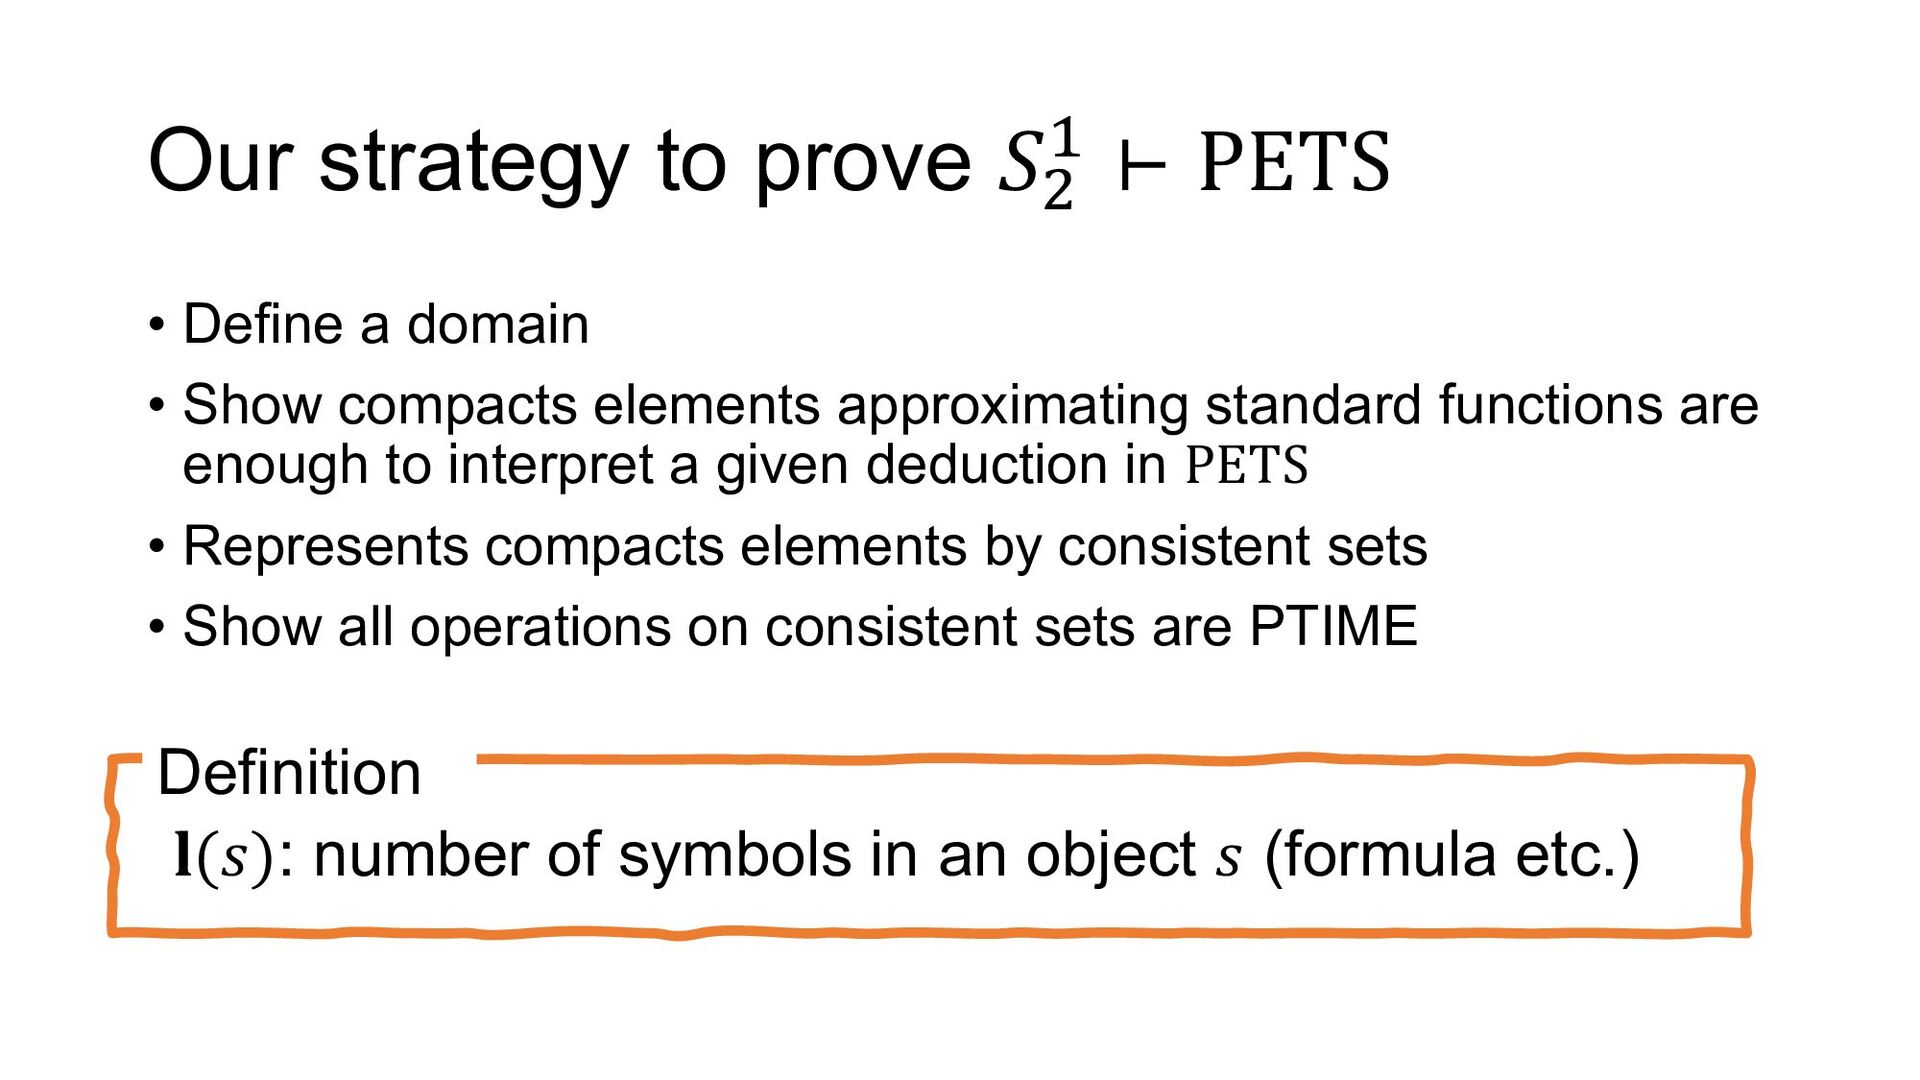
Our strategy to prove 𝑆N O ⊢ PETS • Define
a domain • Show compacts elements approximating standard functions are enough to interpret a given deduction in PETS • Represents compacts elements by consistent sets • Show all operations on consistent sets are PTIME 𝐥(𝑠): number of symbols in an object 𝑠 (formula etc.) Definition -
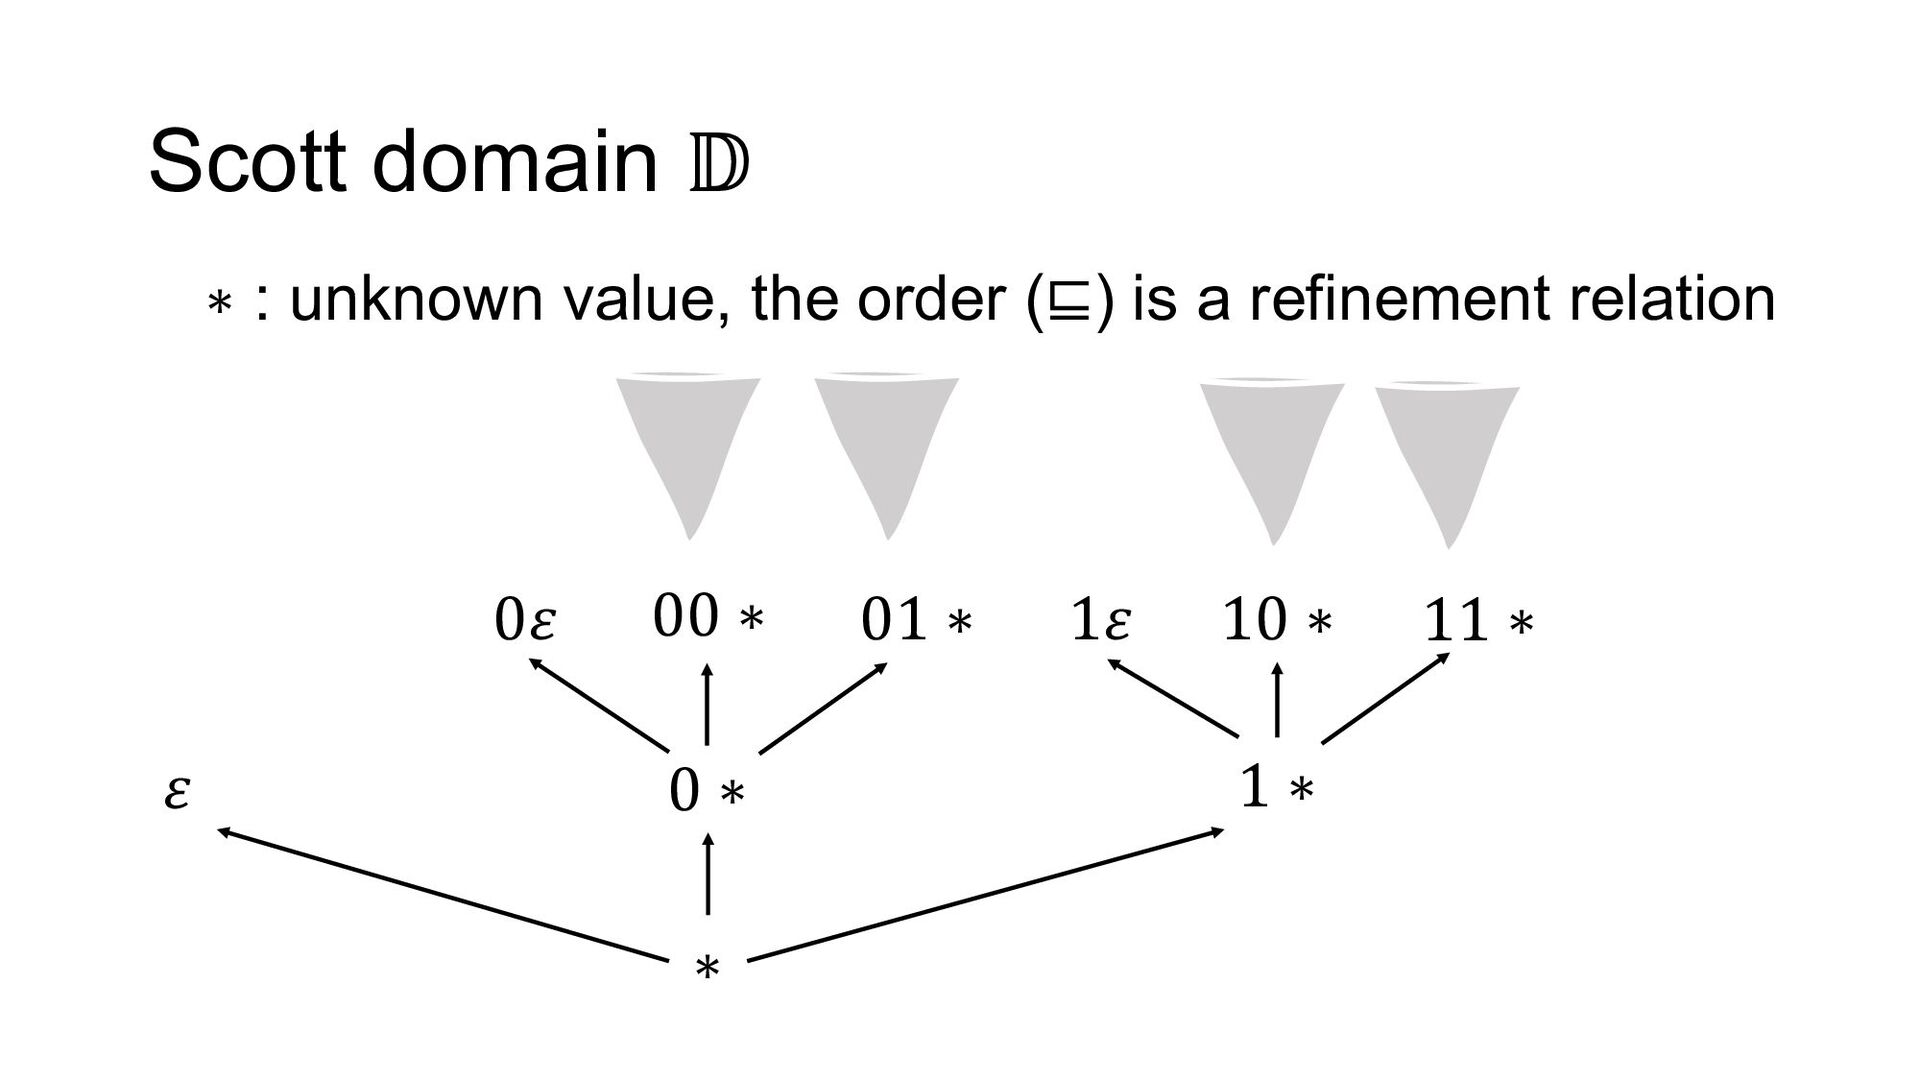
Scott domain 𝔻 ∗ 𝜀 0 ∗ 1 ∗ 0𝜀
00 ∗ 01 ∗ 1𝜀 10 ∗ 11 ∗ ∗ : unknown value, the order (⊑) is a refinement relation -
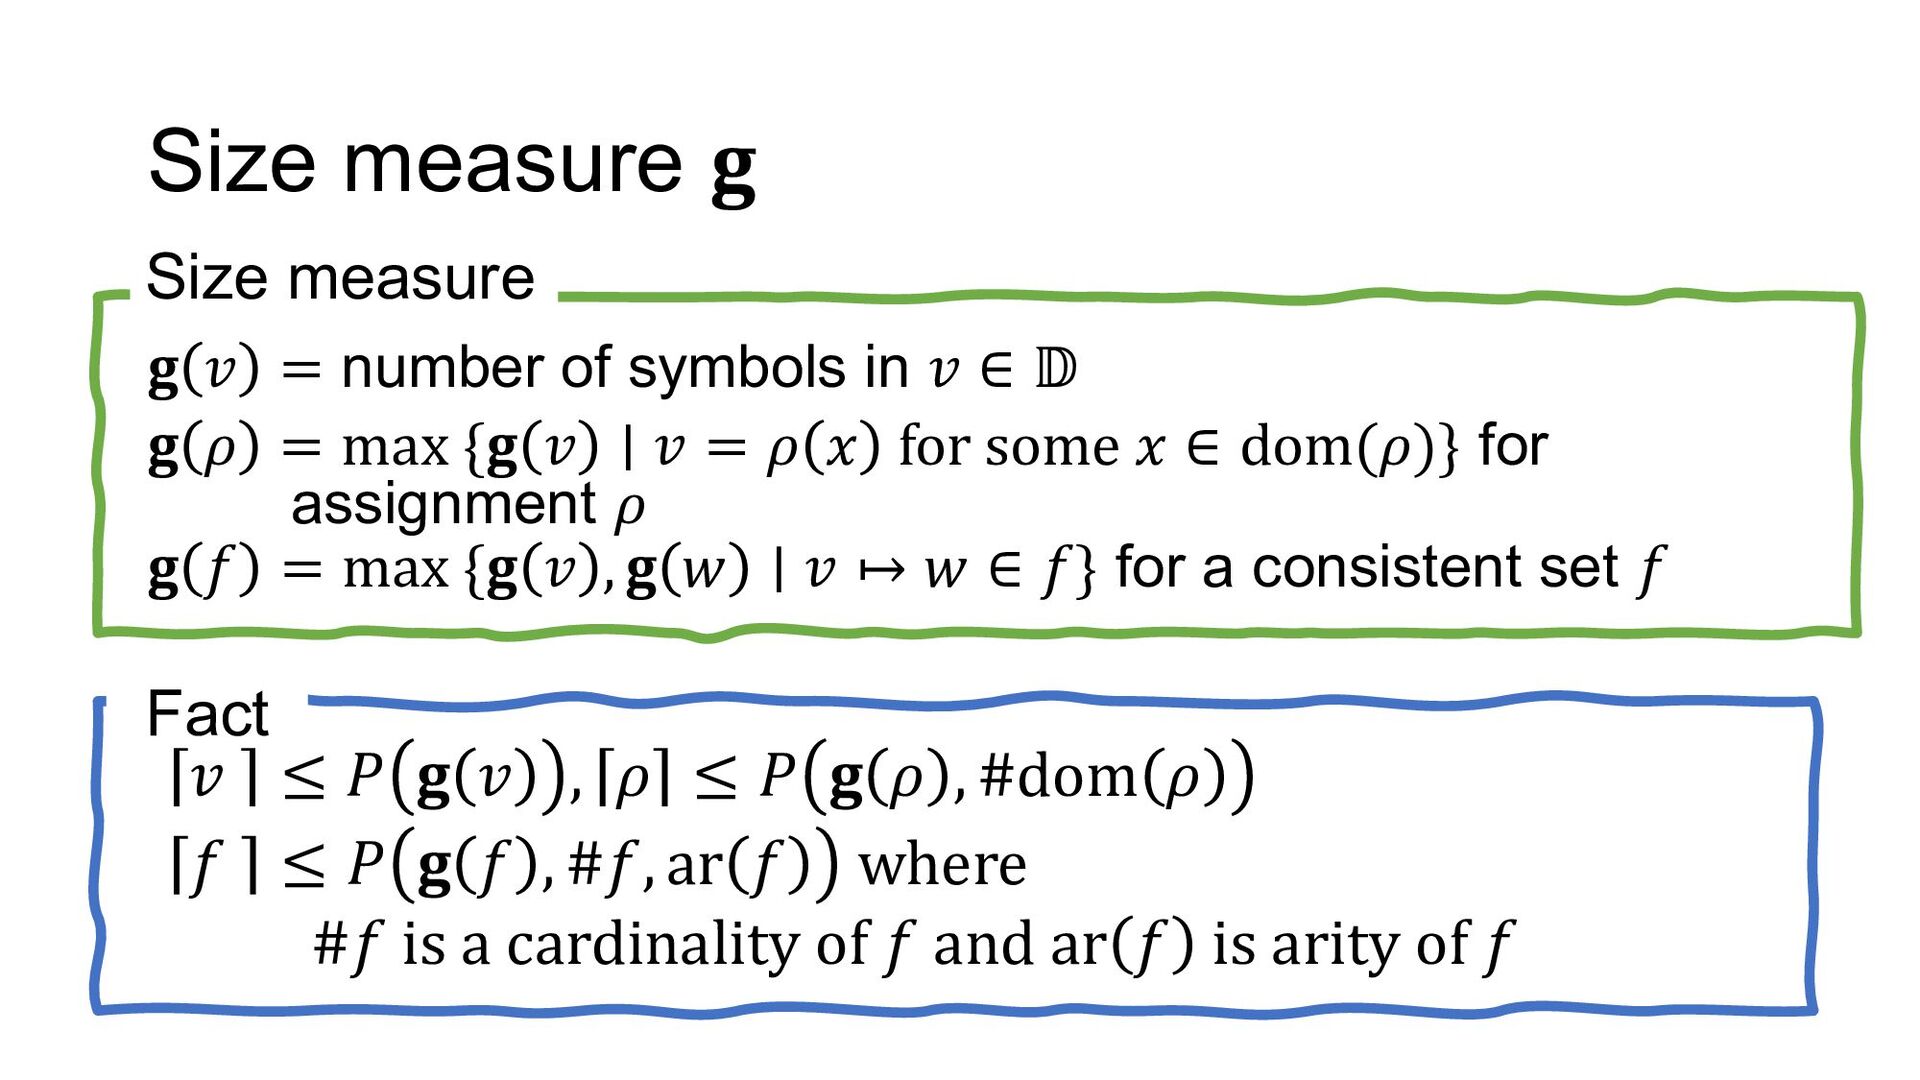
Size measure Size measure 𝐠 𝐠 𝑣 = number of
symbols in 𝑣 ∈ 𝔻 𝐠 𝜌 = max {𝐠 𝑣 ∣ 𝑣 = 𝜌 𝑥 for some 𝑥 ∈ dom(𝜌)} for assignment 𝜌 𝐠 𝑓 = max {𝐠 𝑣 , 𝐠 𝑤 ∣ 𝑣 ↦ 𝑤 ∈ 𝑓} for a consistent set 𝑓 Fact 𝑣 ≤ 𝑃 𝐠 𝑣 , 𝜌 ≤ 𝑃 𝐠 𝜌 , #dom 𝜌 𝑓 ≤ 𝑃 𝐠 𝑓 , #𝑓, ar 𝑓 where #𝑓 is a cardinality of 𝑓 and ar 𝑓 is arity of 𝑓 -
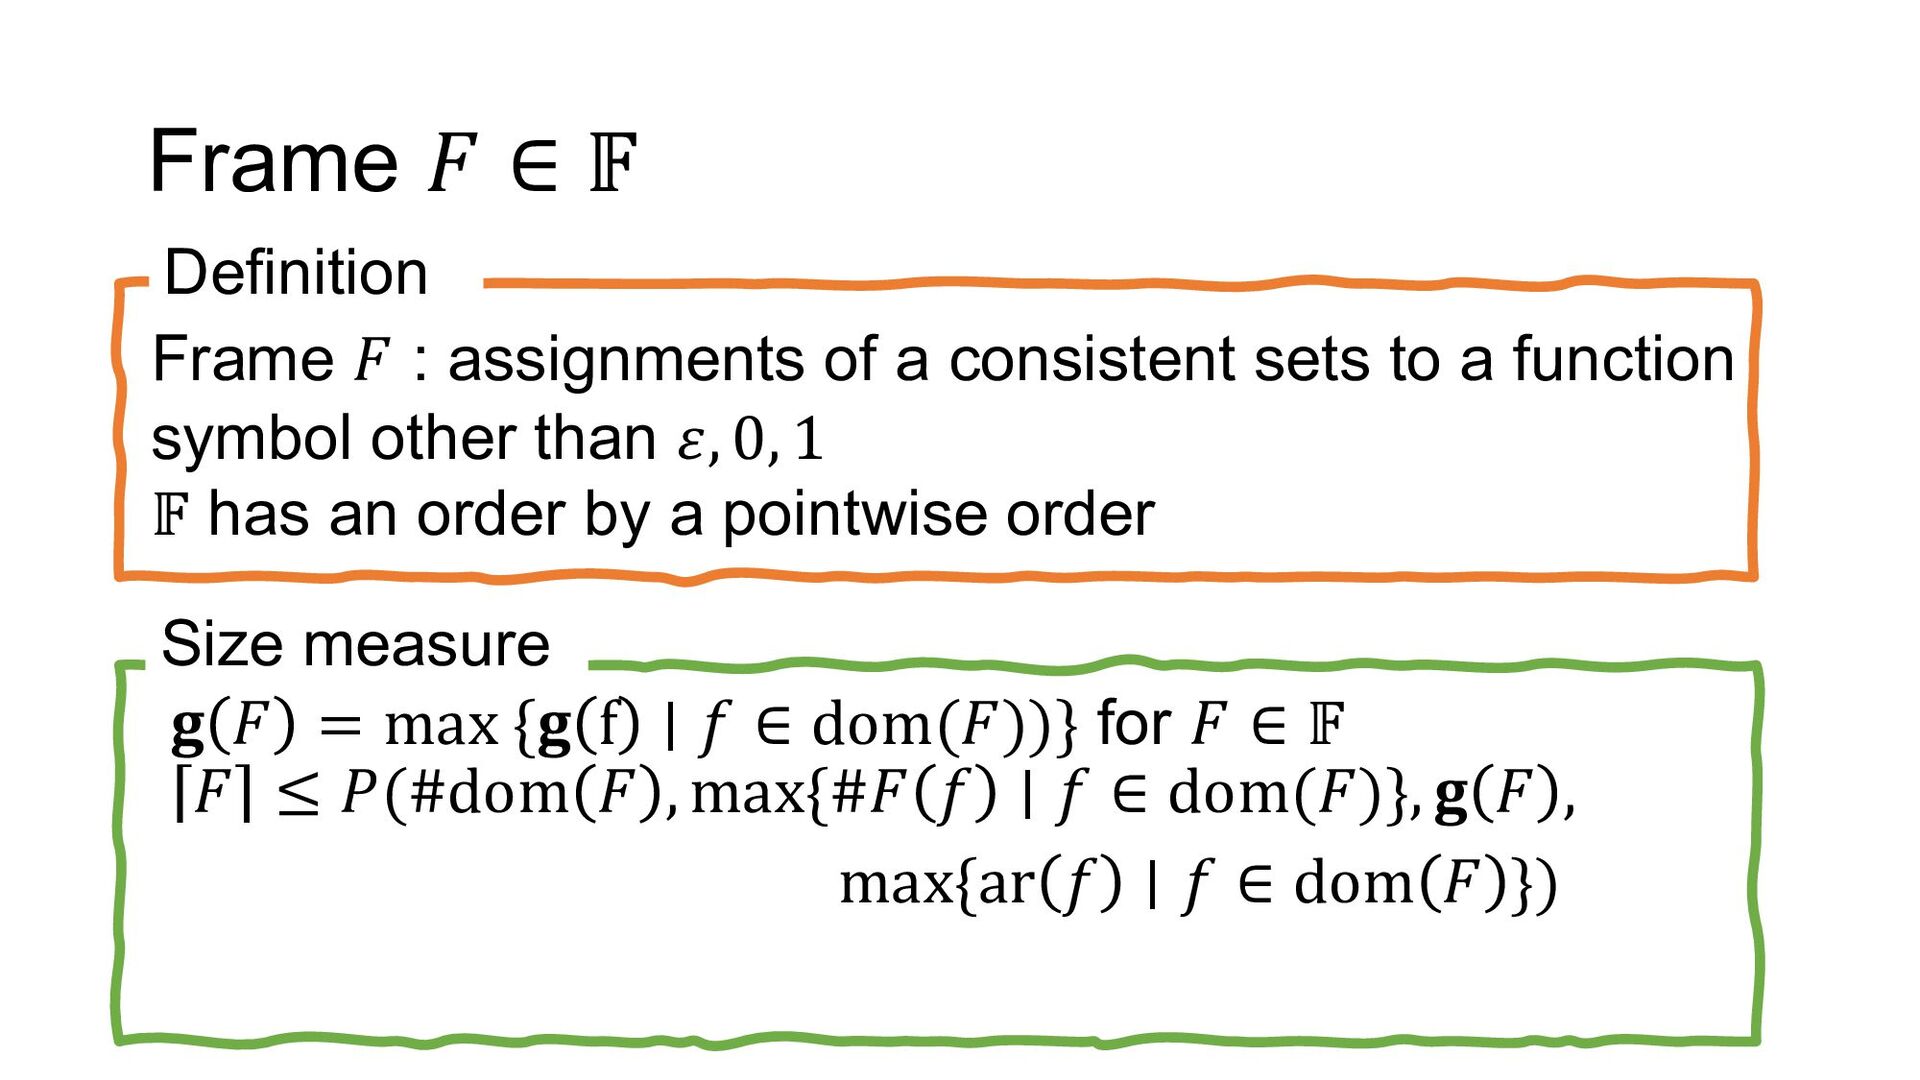
Frame 𝐹 ∈ 𝔽 Frame 𝐹 : assignments of a
consistent sets to a function symbol other than 𝜀, 0, 1 𝔽 has an order by a pointwise order Definition Size measure 𝐠 𝐹 = max {𝐠 f ∣ 𝑓 ∈ dom(𝐹))} for 𝐹 ∈ 𝔽 𝐹 ≤ 𝑃(#dom 𝐹 , max{#𝐹 𝑓 ∣ 𝑓 ∈ dom(𝐹)}, 𝐠 𝐹 , max{ar 𝑓 ∣ 𝑓 ∈ dom 𝐹 }) -
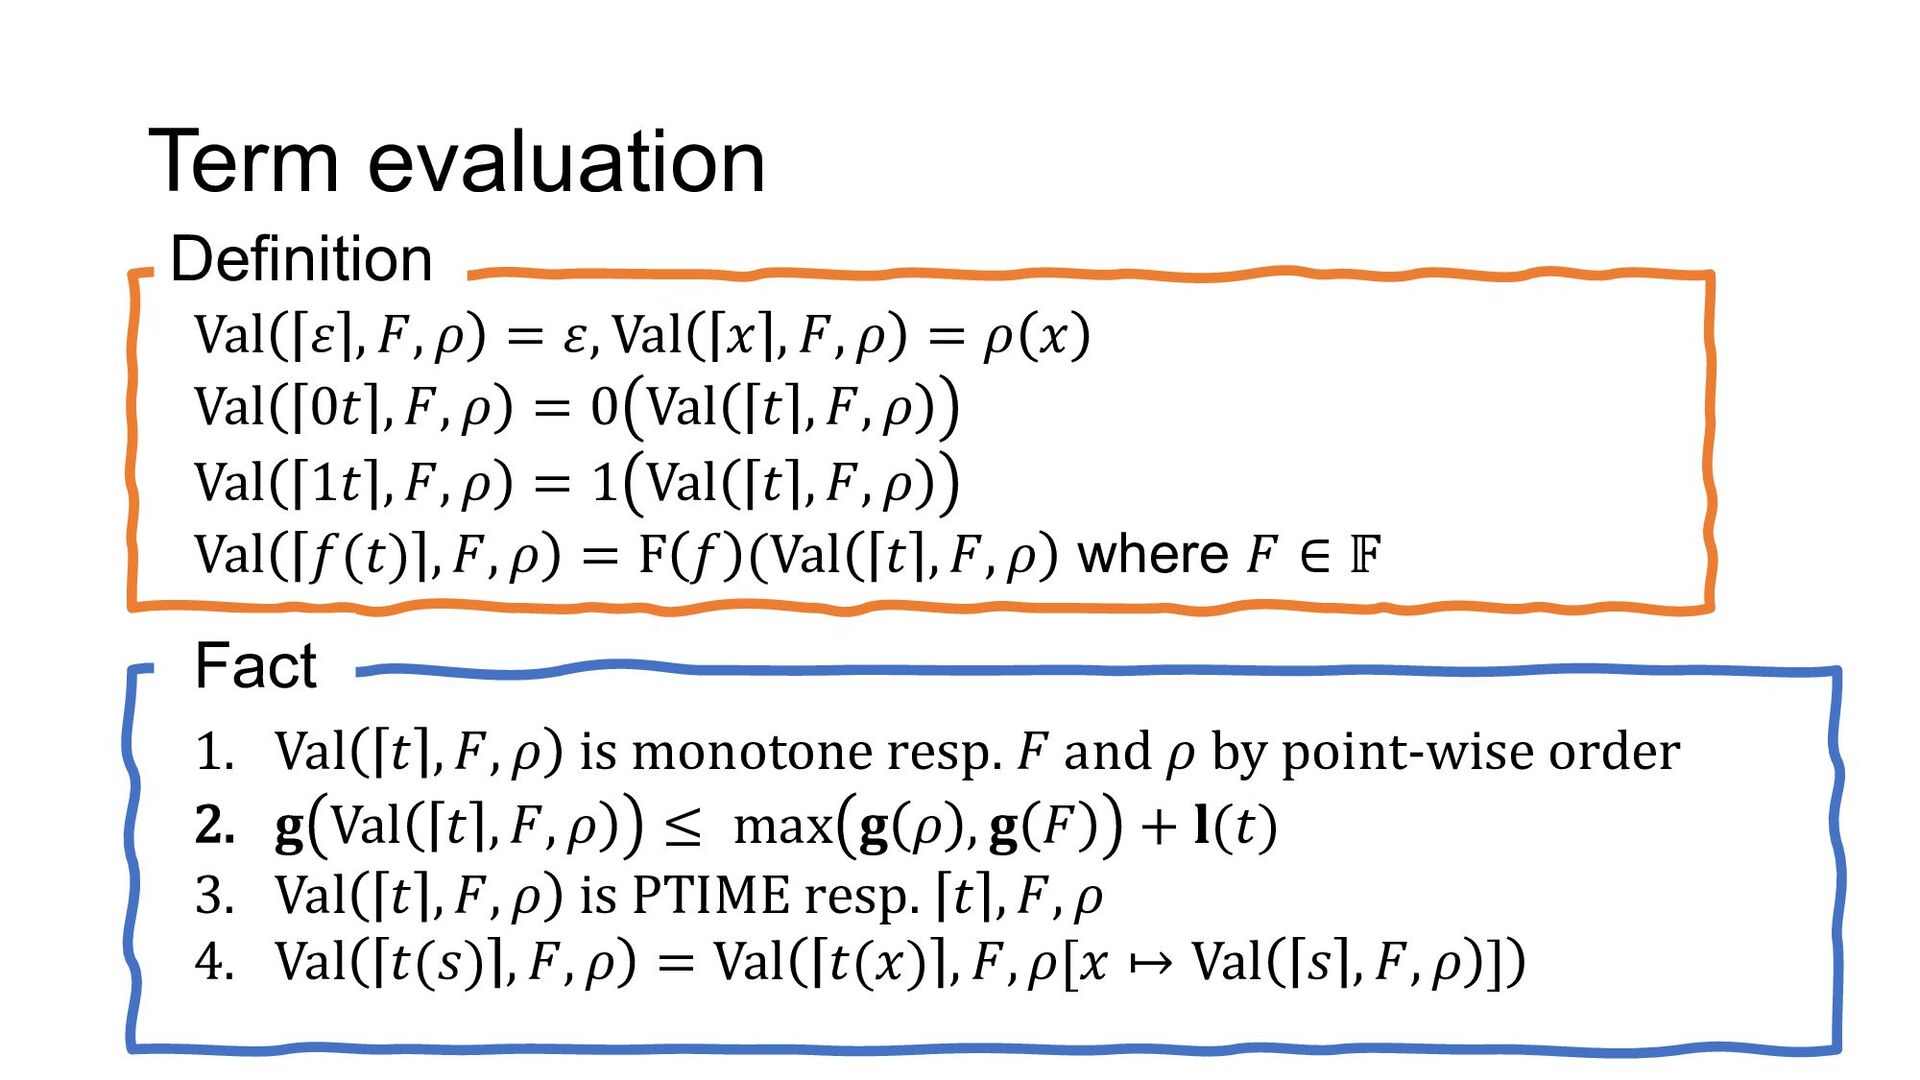
Term evaluation Val 𝜀 , 𝐹, 𝜌 = 𝜀, Val
𝑥 , 𝐹, 𝜌 = 𝜌 𝑥 Val 0𝑡 , 𝐹, 𝜌 = 0 Val 𝑡 , 𝐹, 𝜌 Val 1𝑡 , 𝐹, 𝜌 = 1 Val 𝑡 , 𝐹, 𝜌 Val 𝑓(𝑡) , 𝐹, 𝜌 = F 𝑓 (Val 𝑡 , 𝐹, 𝜌 where 𝐹 ∈ 𝔽 Definition Fact 1. Val 𝑡 , 𝐹, 𝜌 is monotone resp. 𝐹 and 𝜌 by point-wise order 2. 𝐠 Val 𝑡 , 𝐹, 𝜌 ≤ max 𝐠 𝜌 , 𝐠 𝐹 + 𝐥(𝑡) 3. Val 𝑡 , 𝐹, 𝜌 is PTIME resp. 𝑡 , 𝐹, 𝜌 4. Val 𝑡(𝑠) , 𝐹, 𝜌 = Val 𝑡(𝑥) , 𝐹, 𝜌[𝑥 ↦ Val 𝑠 , 𝐹, 𝜌 ] -
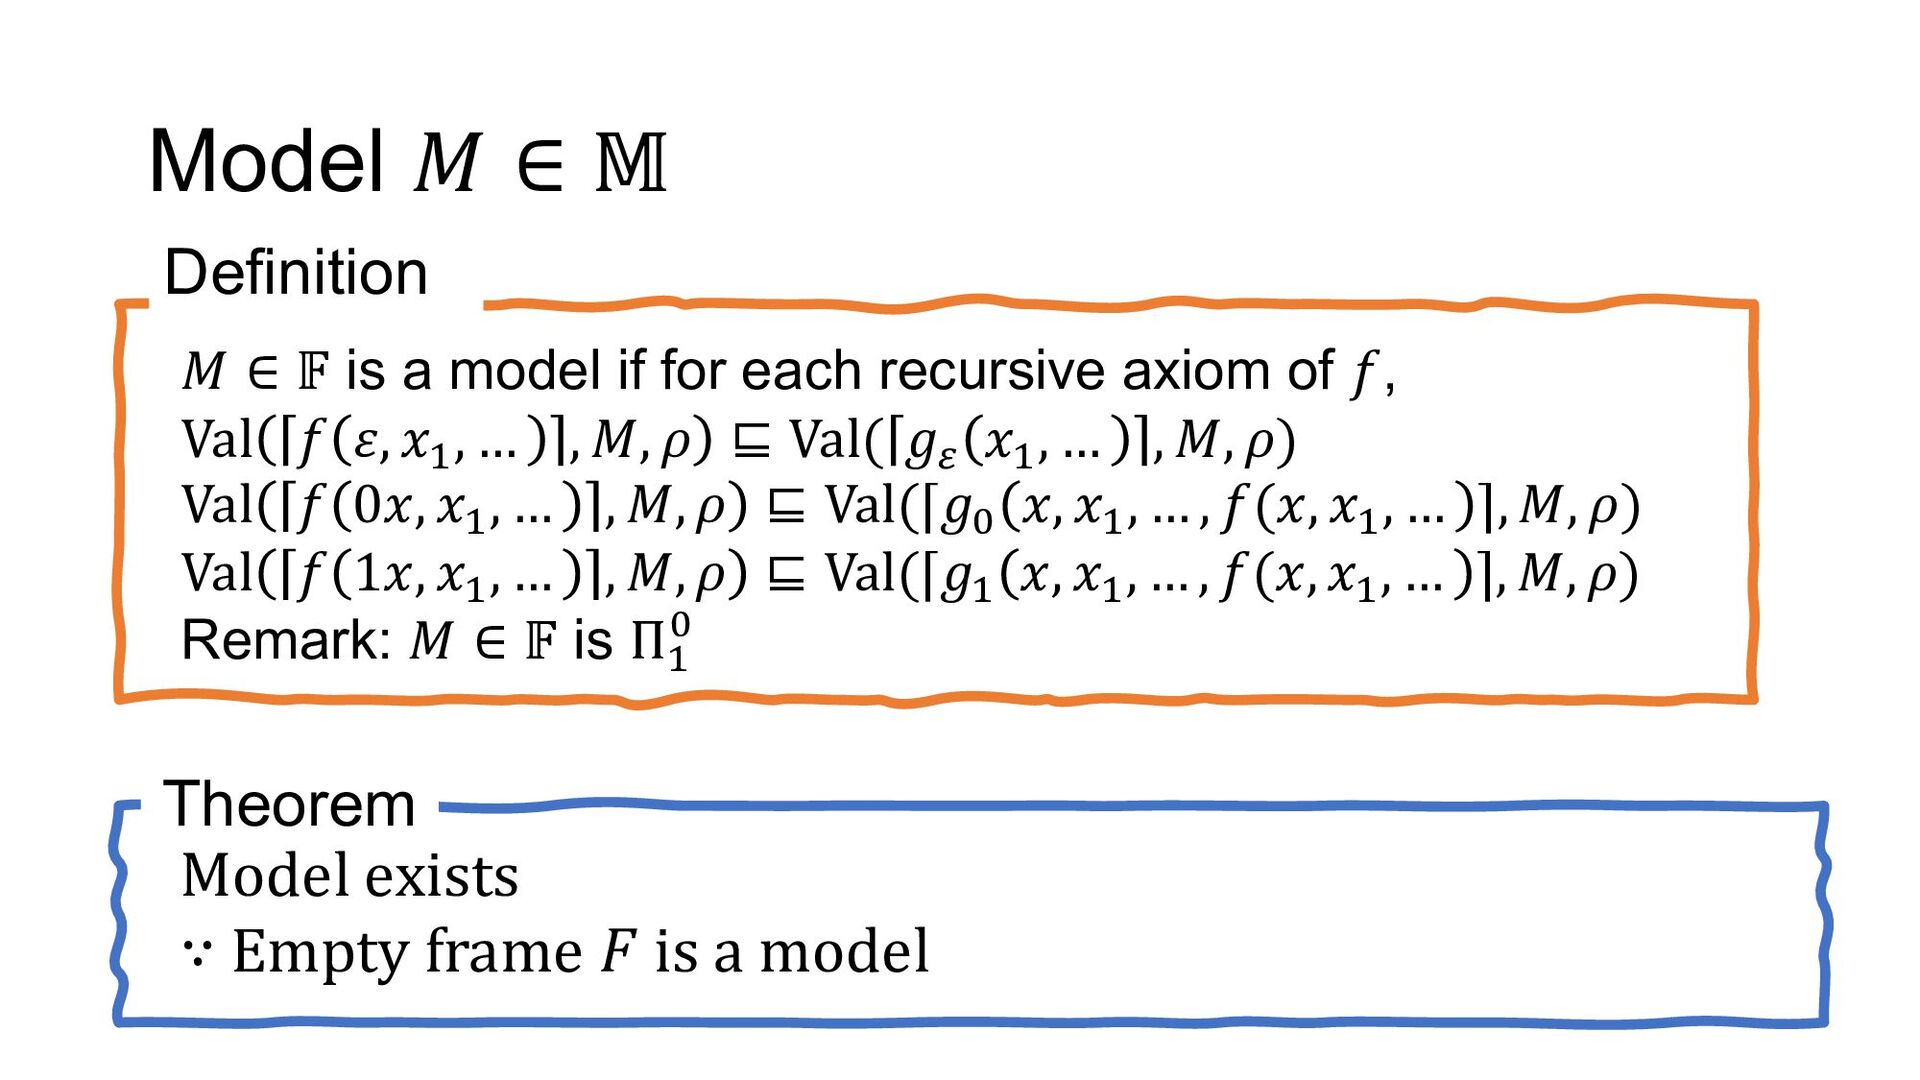
Model 𝑀 ∈ 𝕄 𝑀 ∈ 𝔽 is a model
if for each recursive axiom of 𝑓, Val 𝑓 𝜀, 𝑥# , … , 𝑀, 𝜌 ⊑ Val( 𝑔? 𝑥# , … , 𝑀, 𝜌) Val 𝑓 0𝑥, 𝑥# , … , 𝑀, 𝜌 ⊑ Val(⌈𝑔@ 𝑥, 𝑥# , … , 𝑓(𝑥, 𝑥# , … ⌉, 𝑀, 𝜌) Val 𝑓 1𝑥, 𝑥# , … , 𝑀, 𝜌 ⊑ Val(⌈𝑔# 𝑥, 𝑥# , … , 𝑓(𝑥, 𝑥# , … ⌉, 𝑀, 𝜌) Remark: 𝑀 ∈ 𝔽 is Π# @ Definition Theorem Model exists ∵ Empty frame 𝐹 is a model -
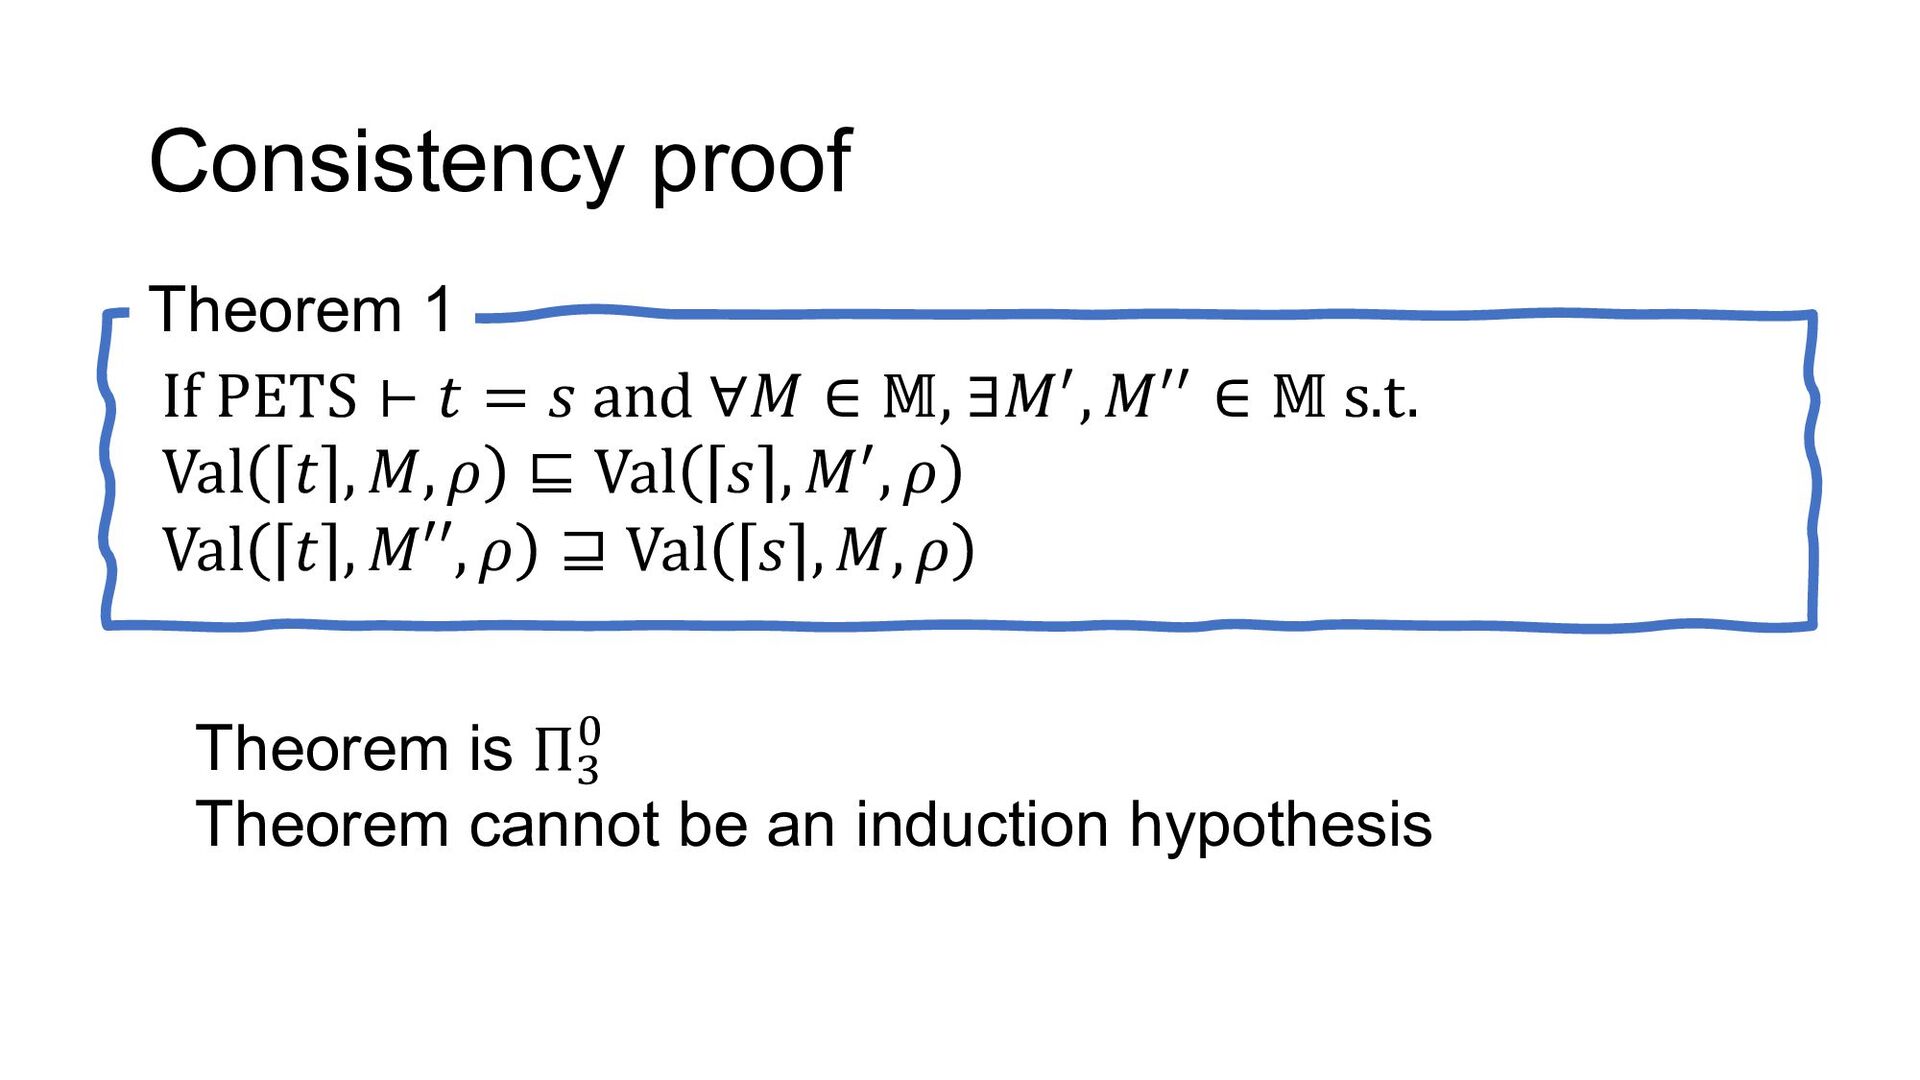
Consistency proof Theorem 1 If PETS ⊢ 𝑡 = 𝑠
and ∀𝑀 ∈ 𝕄, ∃𝑀%, 𝑀%% ∈ 𝕄 s.t. Val 𝑡 , 𝑀, 𝜌 ⊑ Val 𝑠 , 𝑀%, 𝜌 Val 𝑡 , 𝑀′′, 𝜌 ⊒ Val 𝑠 , 𝑀, 𝜌 Theorem is Π& ' Theorem cannot be an induction hypothesis -
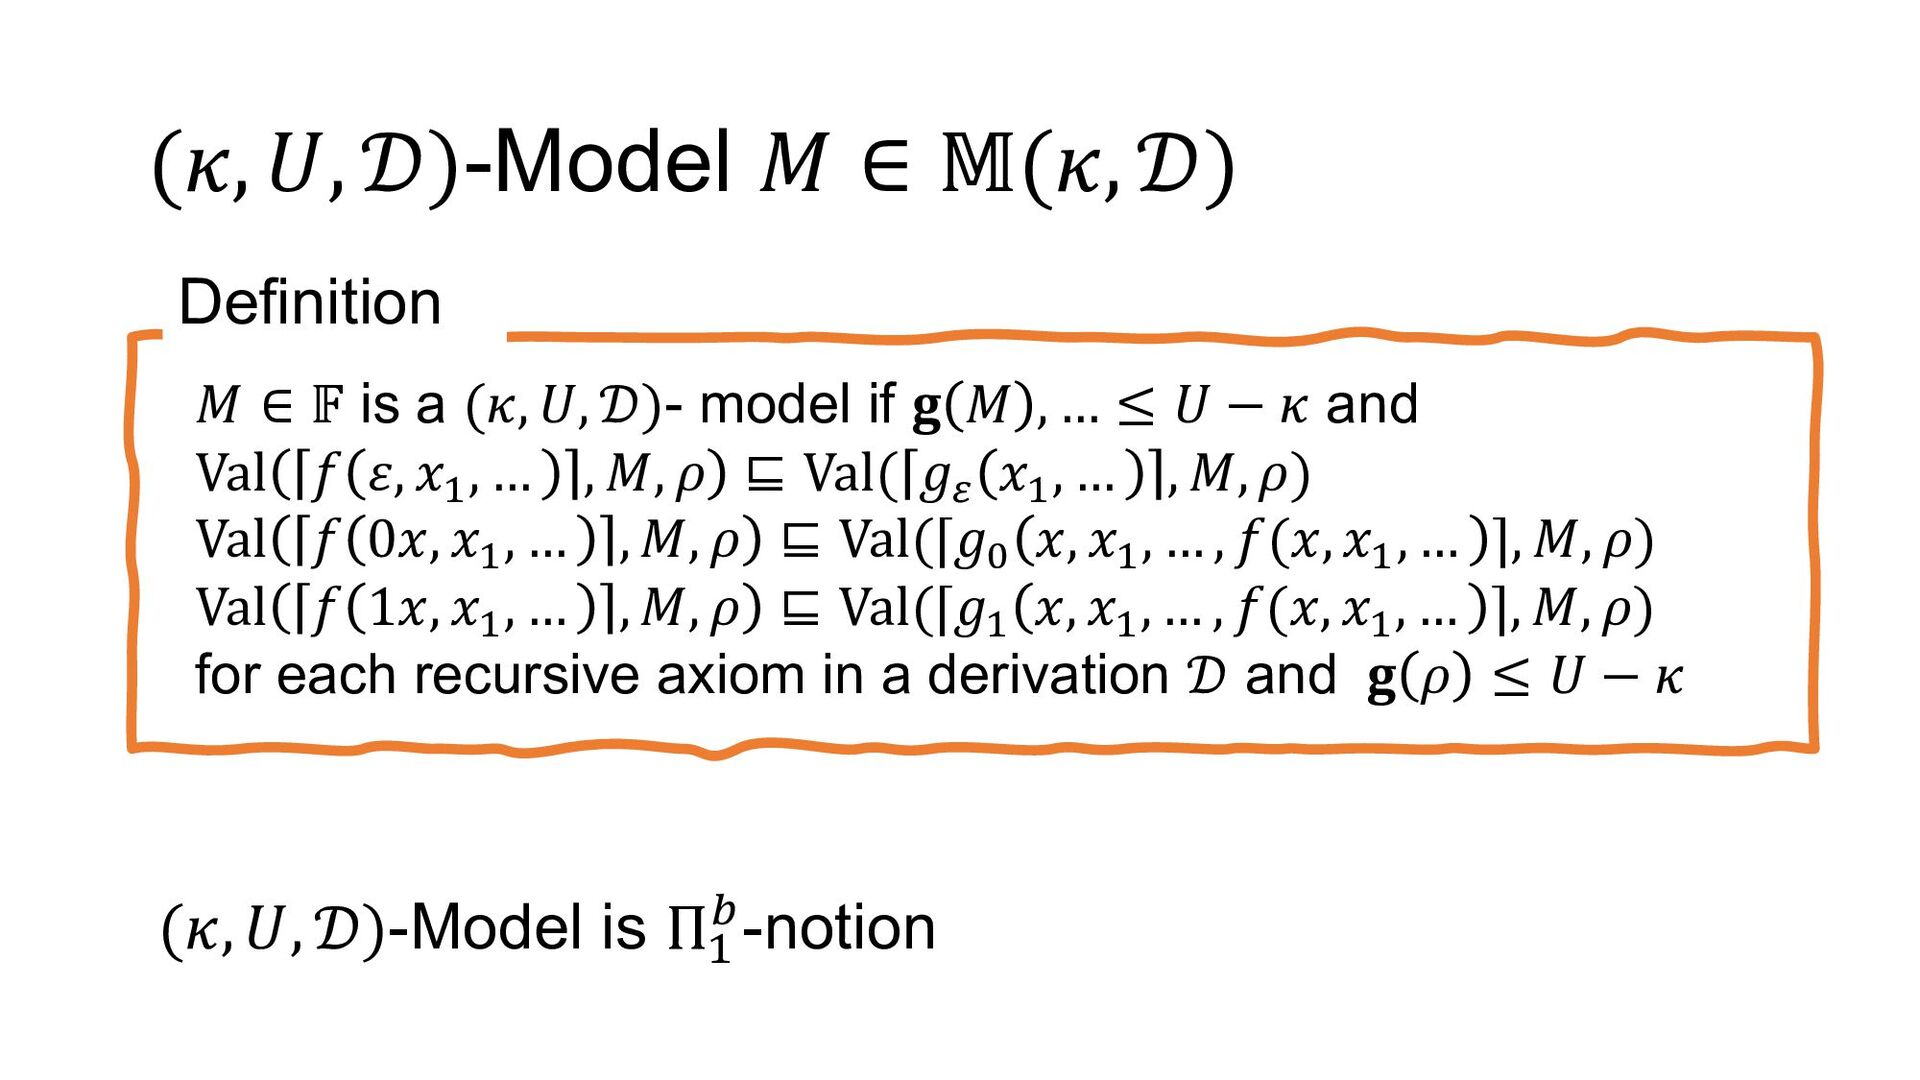
(𝜅, 𝑈, 𝒟)-Model 𝑀 ∈ 𝕄(𝜅, 𝒟) 𝑀 ∈ 𝔽
is a (𝜅, 𝑈, 𝒟)- model if 𝐠 𝑀 , … ≤ 𝑈 − 𝜅 and Val 𝑓 𝜀, 𝑥# , … , 𝑀, 𝜌 ⊑ Val( 𝑔? 𝑥# , … , 𝑀, 𝜌) Val 𝑓 0𝑥, 𝑥# , … , 𝑀, 𝜌 ⊑ Val(⌈𝑔@ 𝑥, 𝑥# , … , 𝑓(𝑥, 𝑥# , … ⌉, 𝑀, 𝜌) Val 𝑓 1𝑥, 𝑥# , … , 𝑀, 𝜌 ⊑ Val(⌈𝑔# 𝑥, 𝑥# , … , 𝑓(𝑥, 𝑥# , … ⌉, 𝑀, 𝜌) for each recursive axiom in a derivation 𝒟 and 𝐠 𝜌 ≤ 𝑈 − 𝜅 Definition (𝜅, 𝑈, 𝒟)-Model is Π$ (-notion -
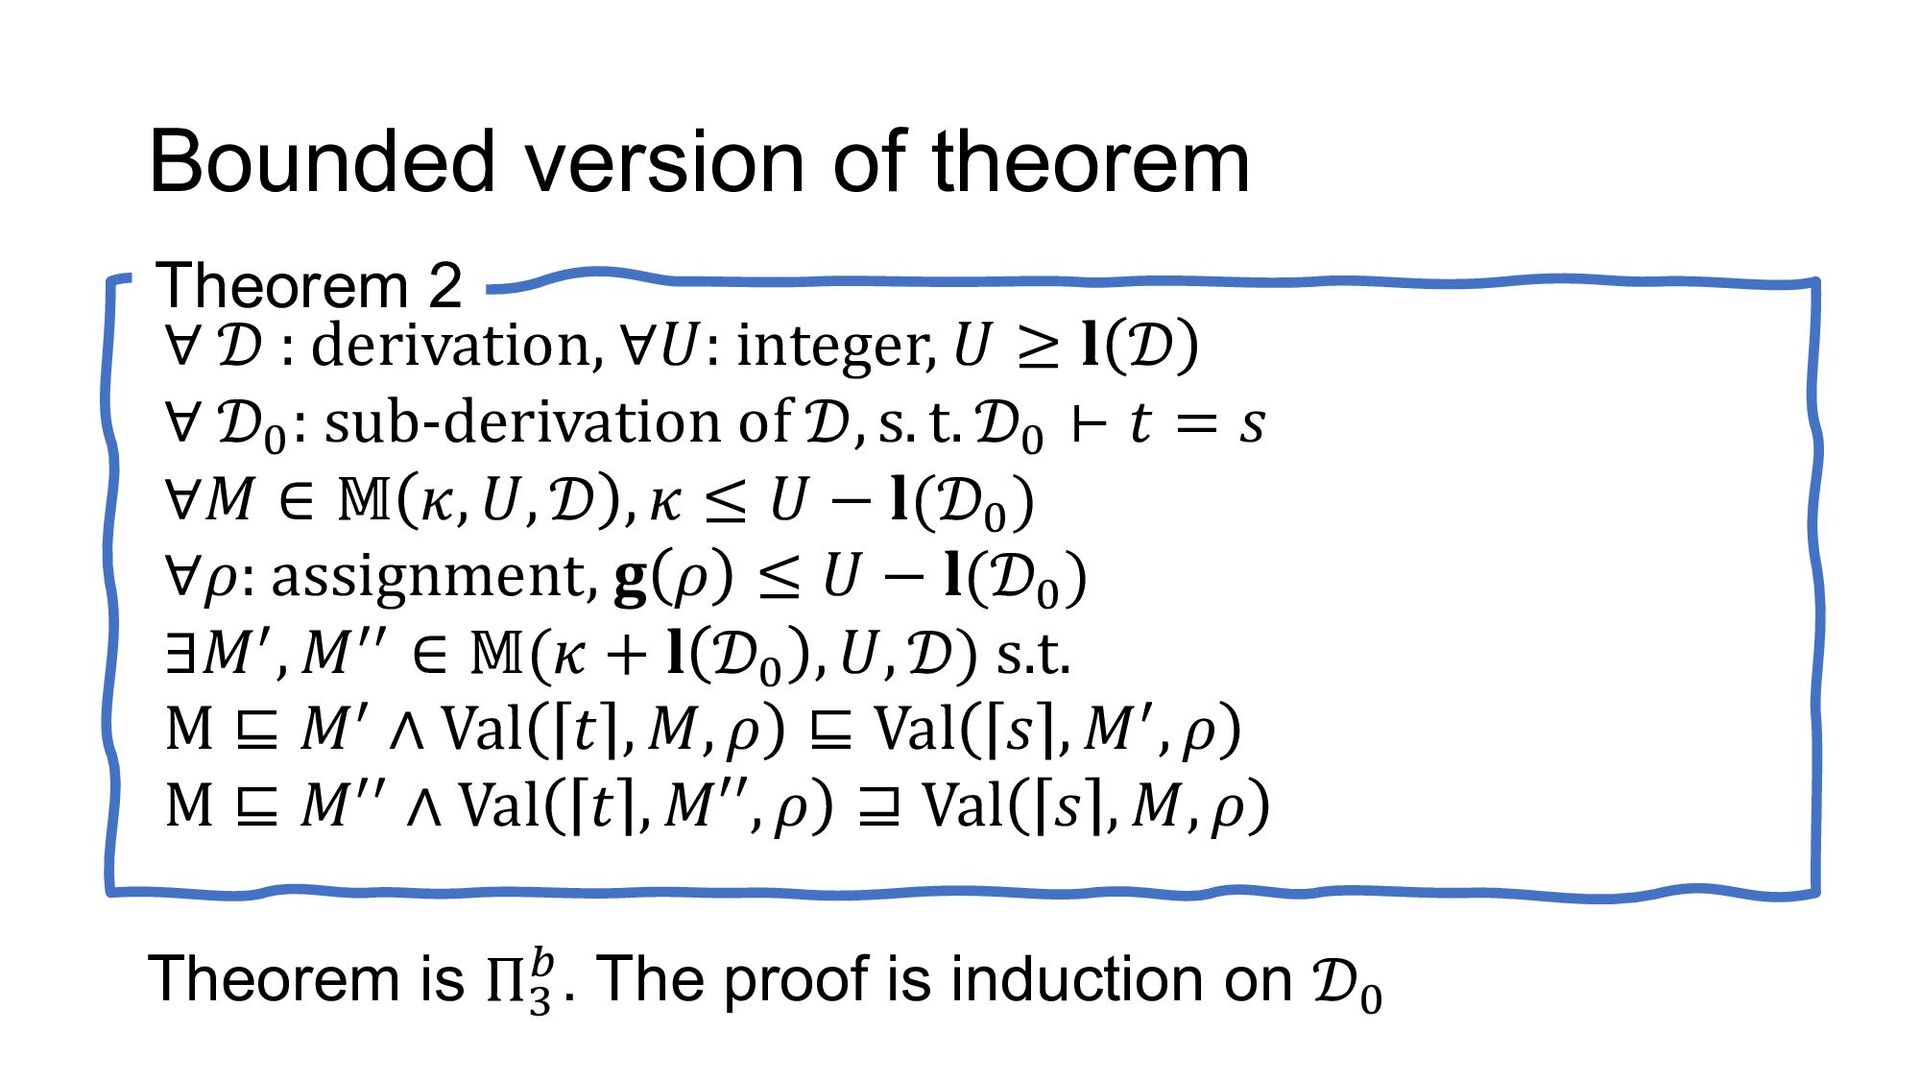
Bounded version of theorem Theorem 2 ∀ 𝒟 : derivation,
∀𝑈: integer, 𝑈 ≥ 𝐥 𝒟 ∀ 𝒟' : sub-derivation of 𝒟, s. t. 𝒟' ⊢ 𝑡 = 𝑠 ∀𝑀 ∈ 𝕄 𝜅, 𝑈, 𝒟 , 𝜅 ≤ 𝑈 − 𝐥(𝒟' ) ∀𝜌: assignment, 𝐠 𝜌 ≤ 𝑈 − 𝐥(𝒟' ) ∃𝑀%, 𝑀%% ∈ 𝕄(𝜅 + 𝐥 𝒟' , 𝑈, 𝒟) s.t. M ⊑ 𝑀% ∧ Val 𝑡 , 𝑀, 𝜌 ⊑ Val 𝑠 , 𝑀%, 𝜌 M ⊑ 𝑀%% ∧ Val 𝑡 , 𝑀′′, 𝜌 ⊒ Val 𝑠 , 𝑀, 𝜌 Theorem is Π& (. The proof is induction on 𝒟' -
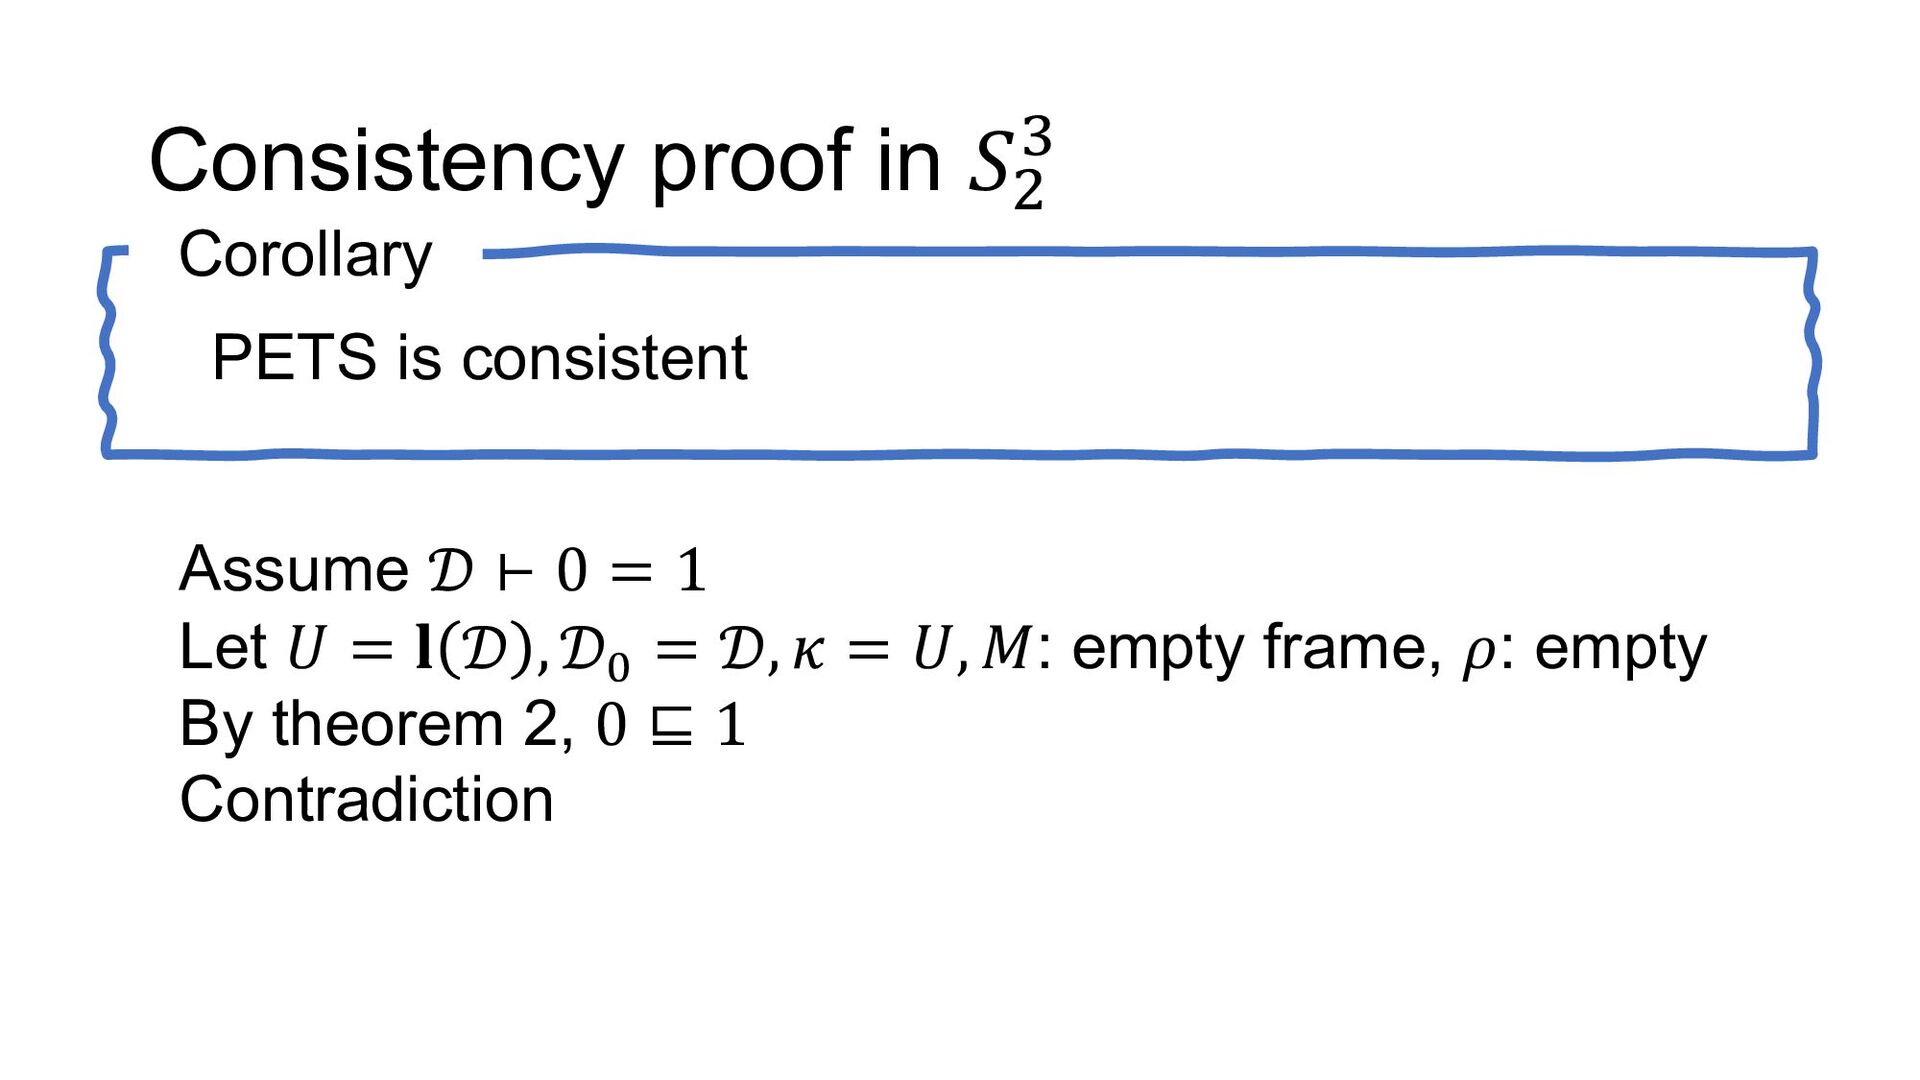
Consistency proof in 𝑆N z Corollary PETS is consistent Assume
𝒟 ⊢ 0 = 1 Let 𝑈 = 𝐥 𝒟 , 𝒟' = 𝒟, 𝜅 = 𝑈, 𝑀: empty frame, 𝜌: empty By theorem 2, 0 ⊑ 1 Contradiction -
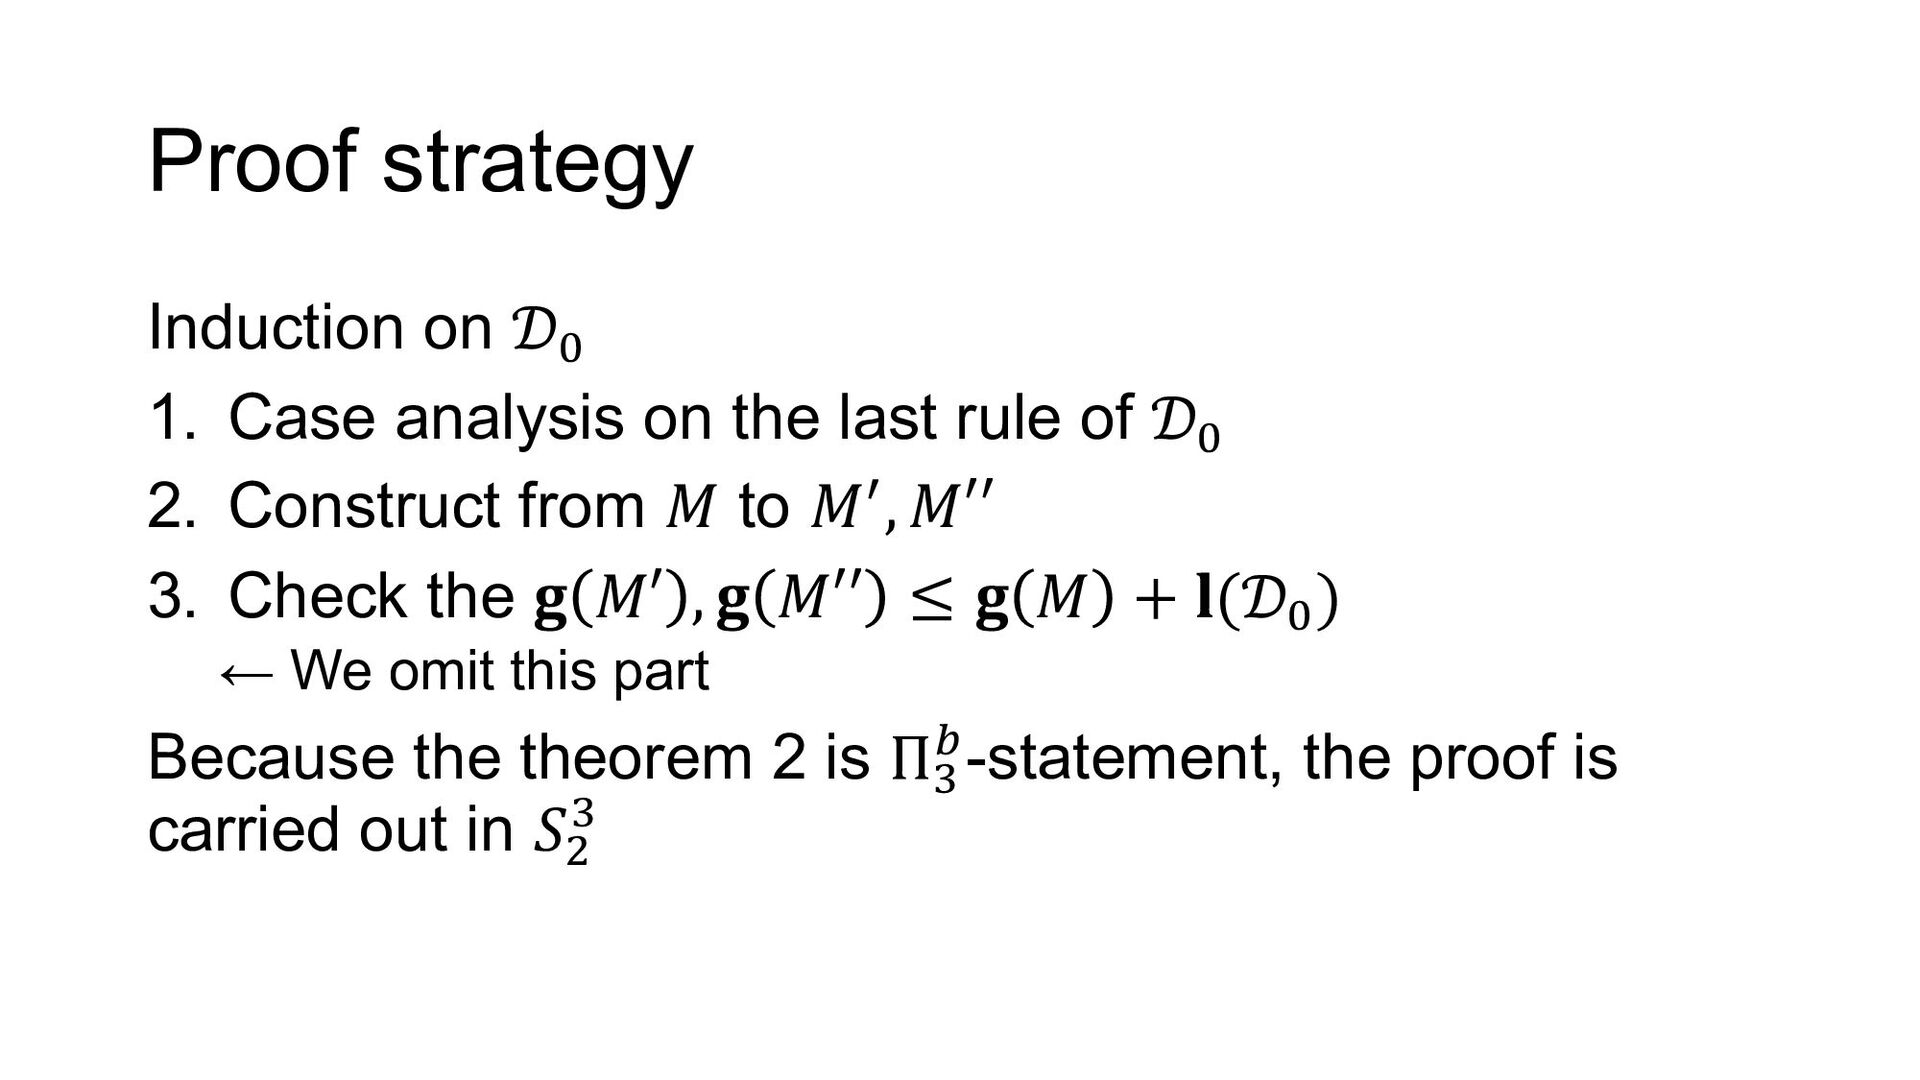
Proof strategy Induction on 𝒟' 1. Case analysis on the
last rule of 𝒟' 2. Construct from 𝑀 to 𝑀%, 𝑀′′ 3. Check the 𝐠 𝑀′ , 𝐠 𝑀′′ ≤ 𝐠 𝑀 + 𝐥(𝒟' ) ← We omit this part Because the theorem 2 is Π& (-statement, the proof is carried out in 𝑆! & -
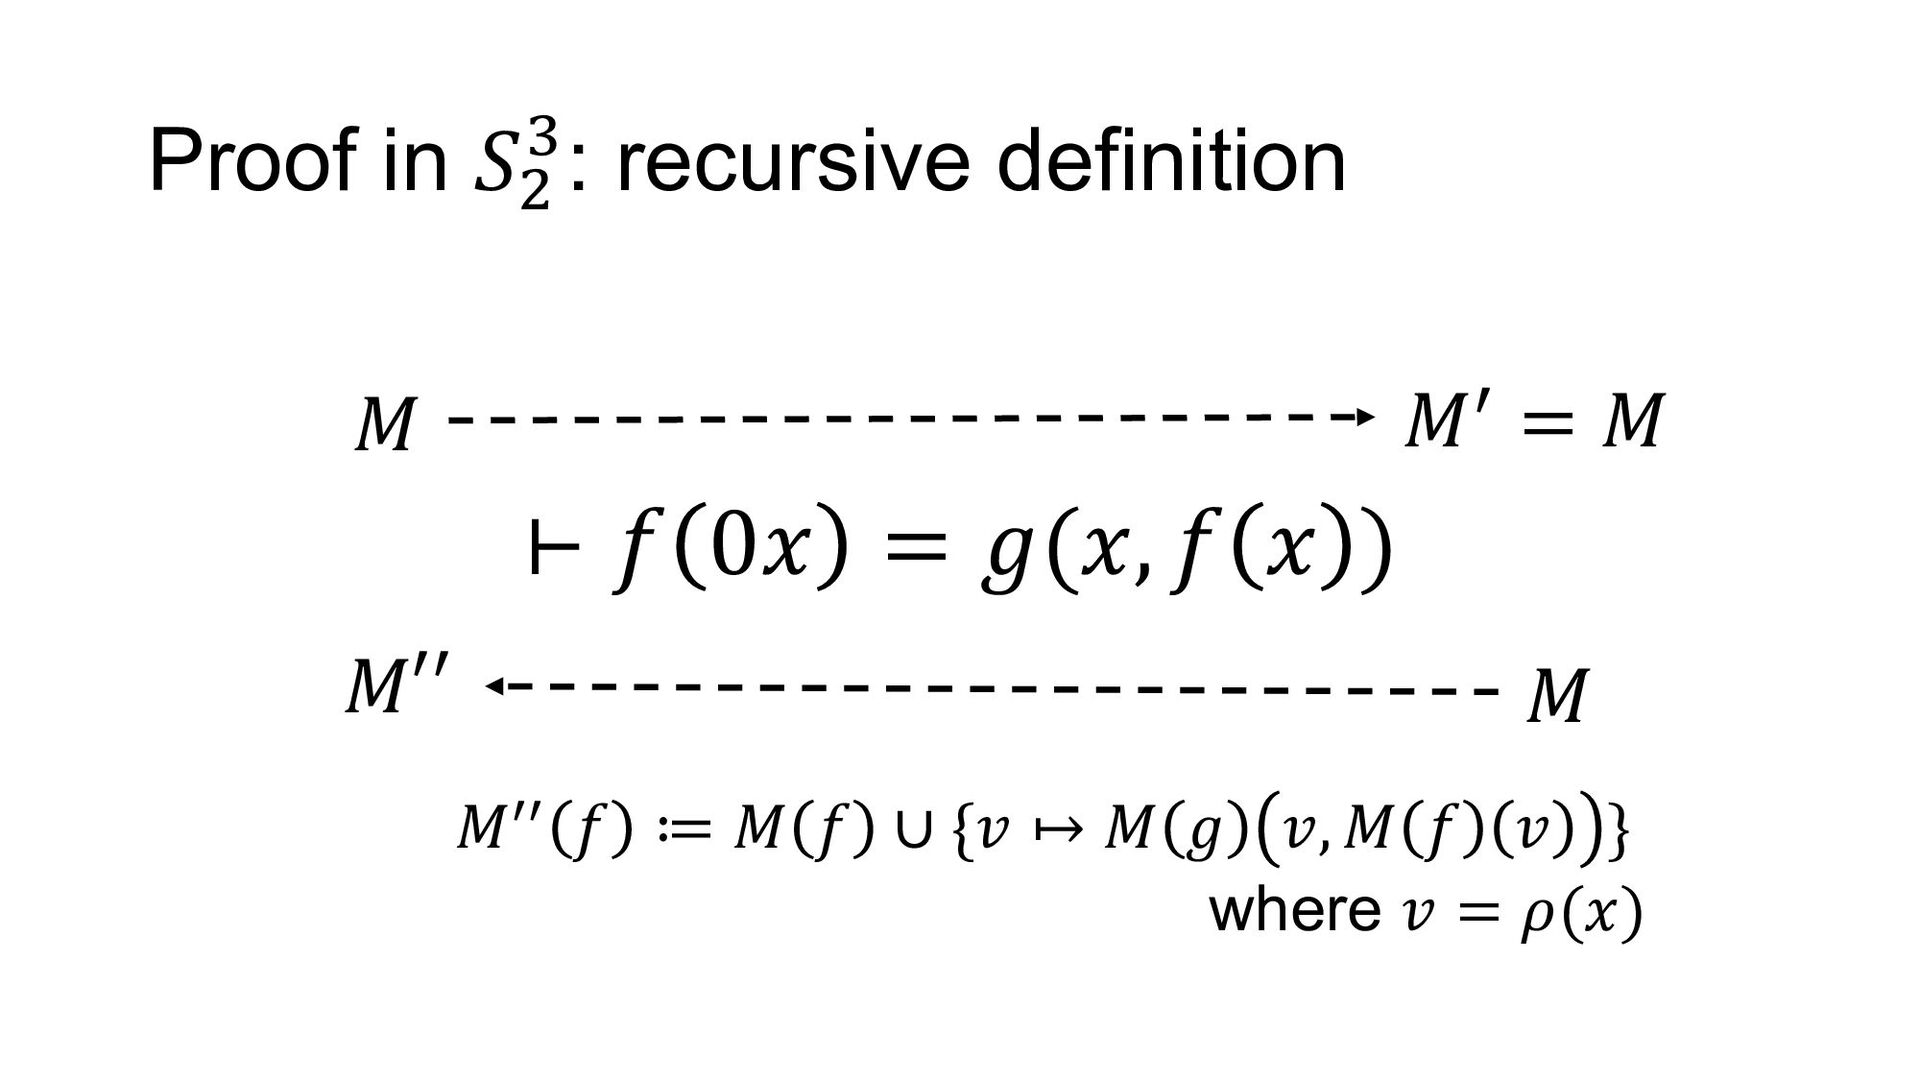
Proof in 𝑆N z: recursive definition ⊢ 𝑓 0𝑥 =
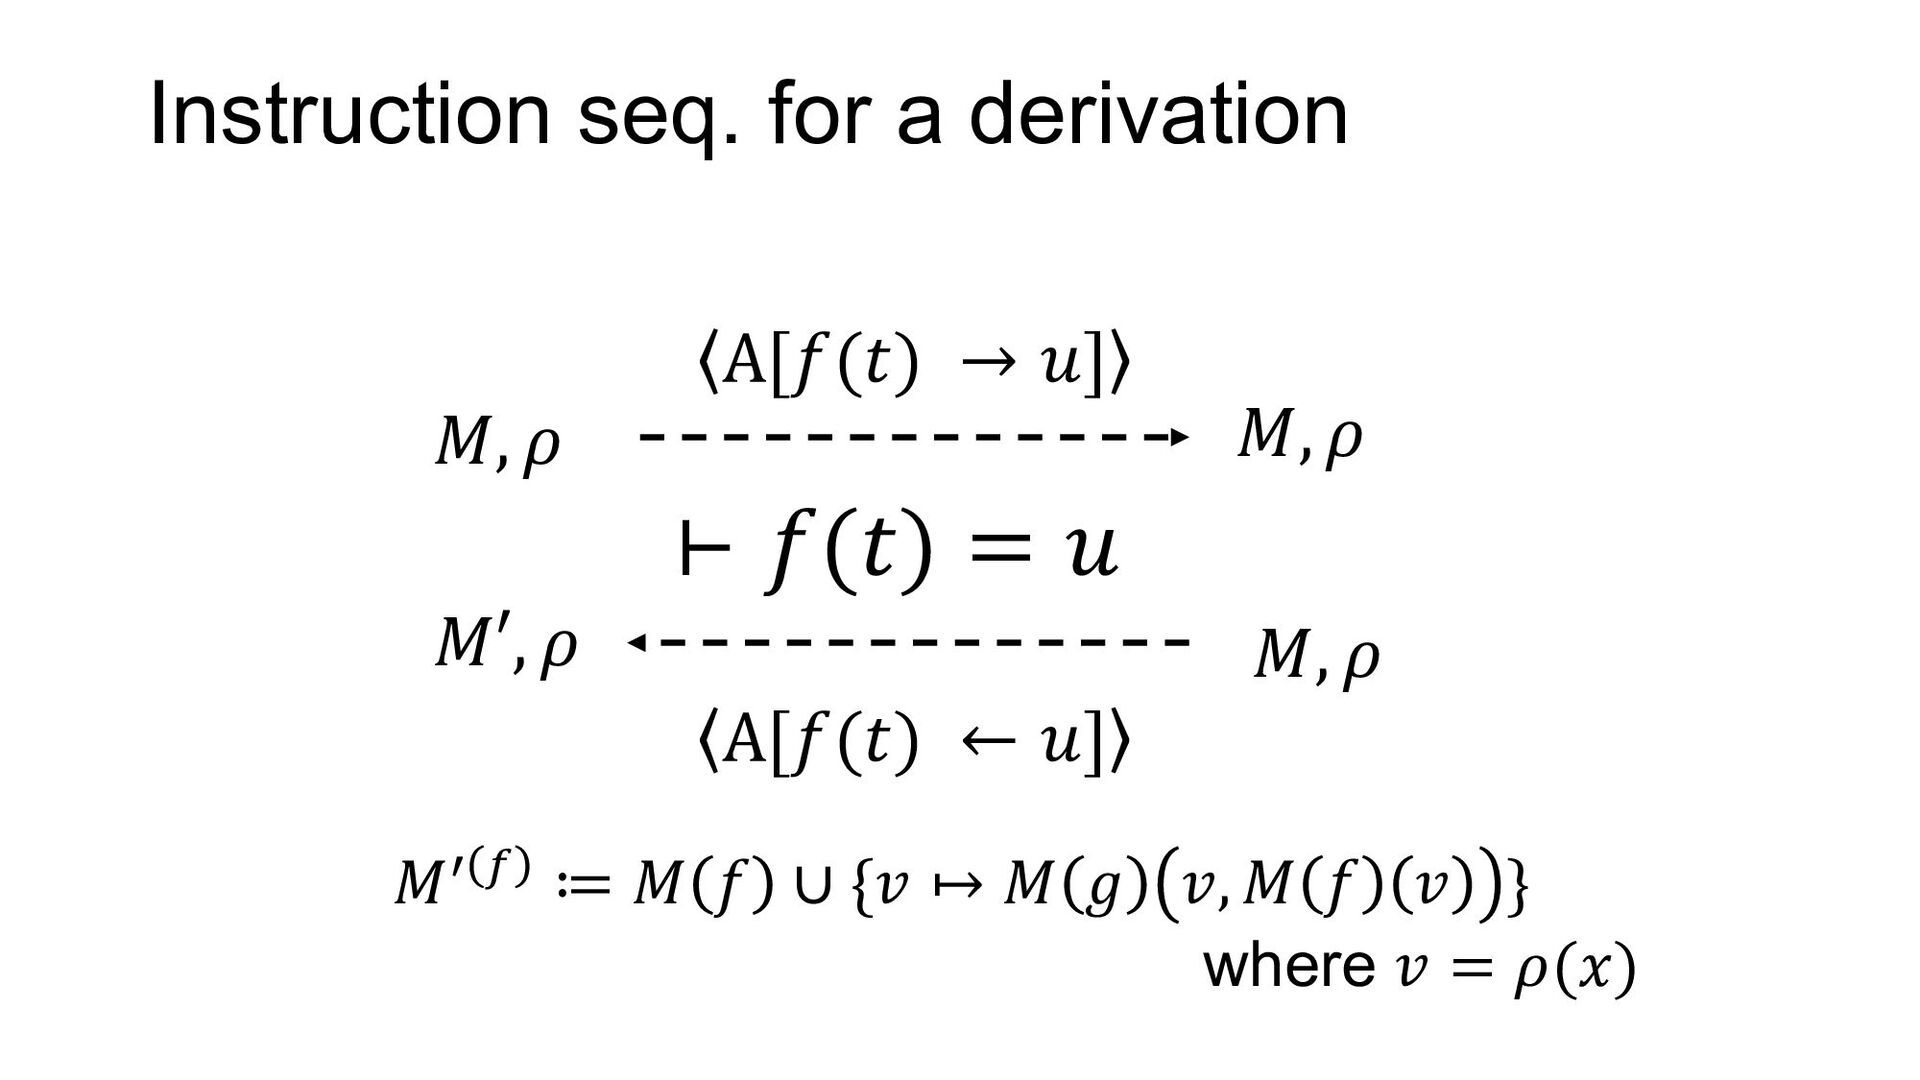
𝑔(𝑥, 𝑓 𝑥 ) 𝑀 𝑀′′ 𝑀%% 𝑓 ≔ 𝑀 𝑓 ∪ {𝑣 ↦ 𝑀 𝑔 𝑣, 𝑀 𝑓 𝑣 } where 𝑣 = 𝜌(𝑥) 𝑀 𝑀# = 𝑀 -
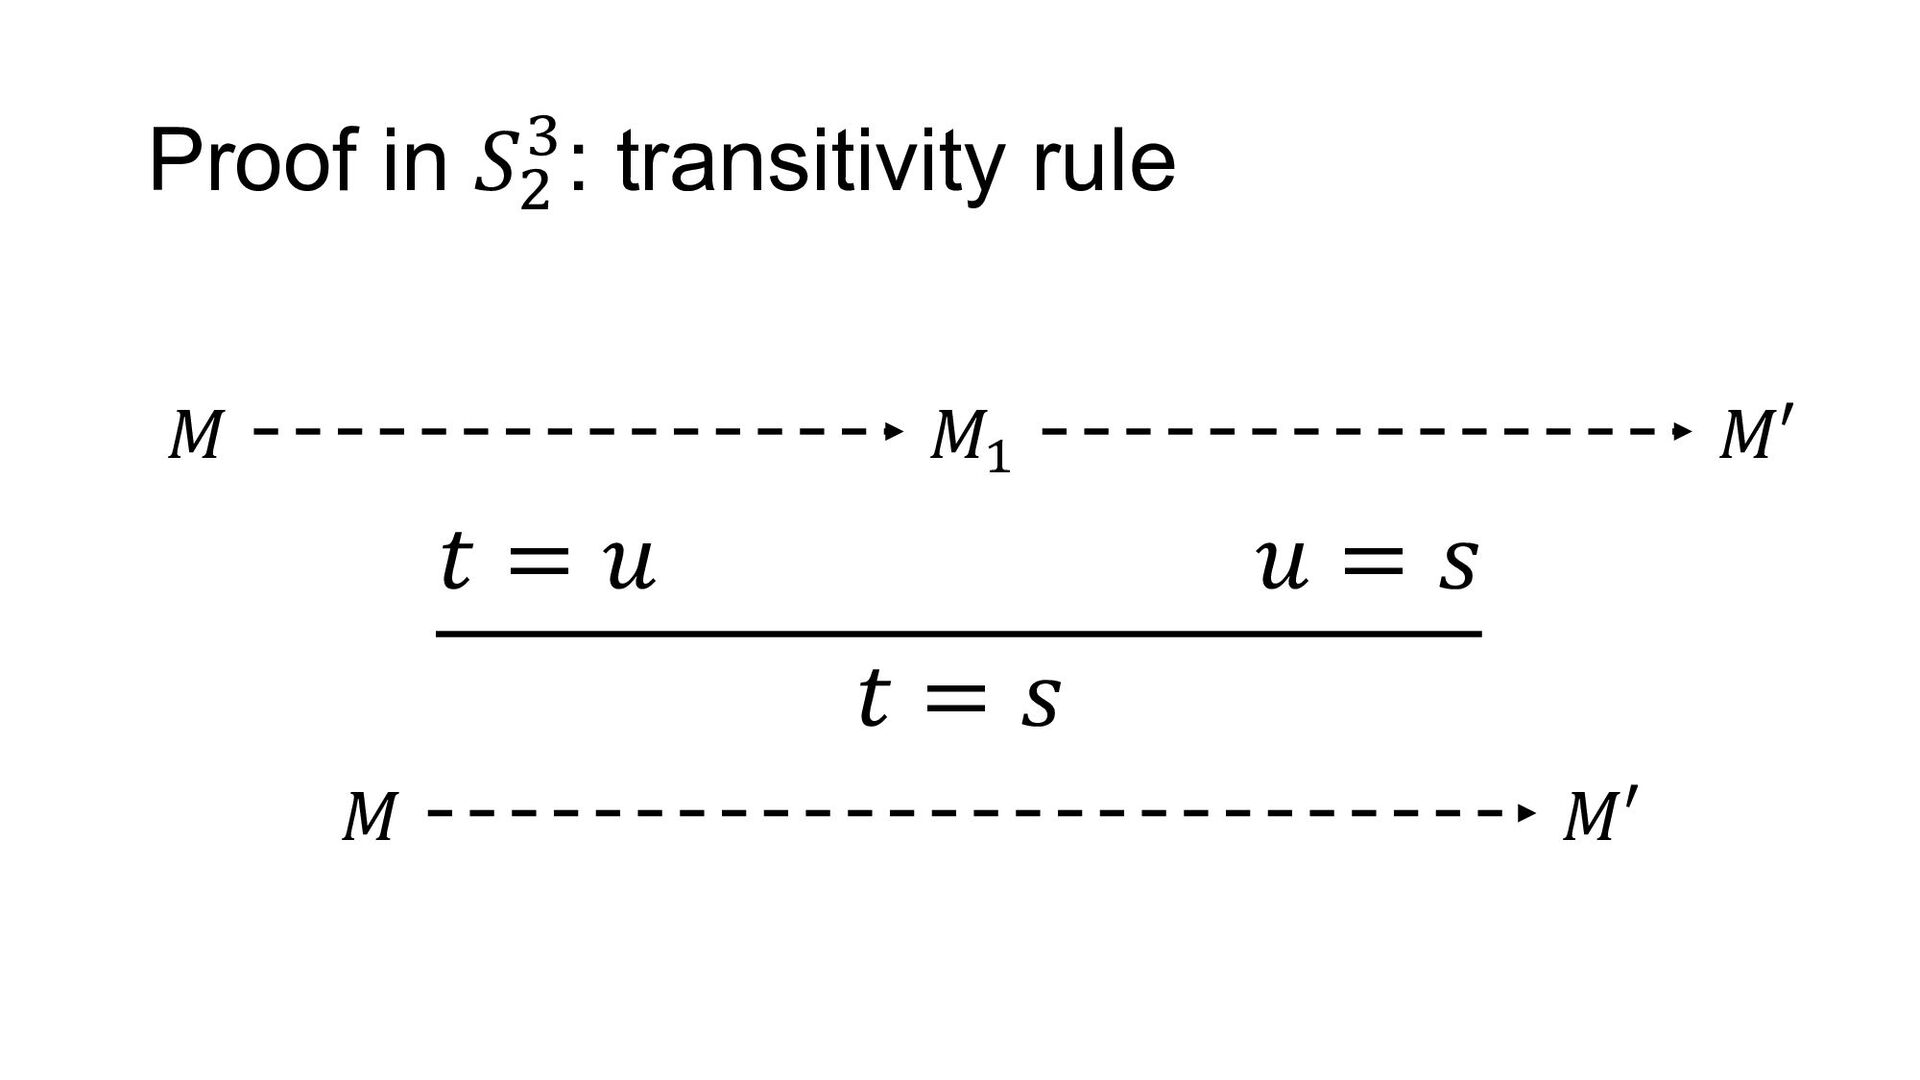
Proof in 𝑆N z: transitivity rule 𝑡 = 𝑢 𝑢
= 𝑠 𝑡 = 𝑠 𝑀 𝑀! 𝑀′ 𝑀 𝑀′ -
Proof in 𝑆N z : compatibility rule 𝑡 = 𝑢
𝑠 𝑡 = 𝑠 𝑢 𝑀 𝑀′ 𝑀 𝑀′ Val 𝑠 𝑡 , 𝑀, 𝜌 = Val 𝑠 𝑥 , 𝑀, 𝜌 𝑥 ↦ Val 𝑡 , 𝑀, 𝜌 ⊑ Val 𝑠 𝑥 , 𝑀, 𝜌 𝑥 ↦ Val 𝑢 , 𝑀C, 𝜌 ⊑ Val 𝑠 𝑢 , 𝑀C, 𝜌 -
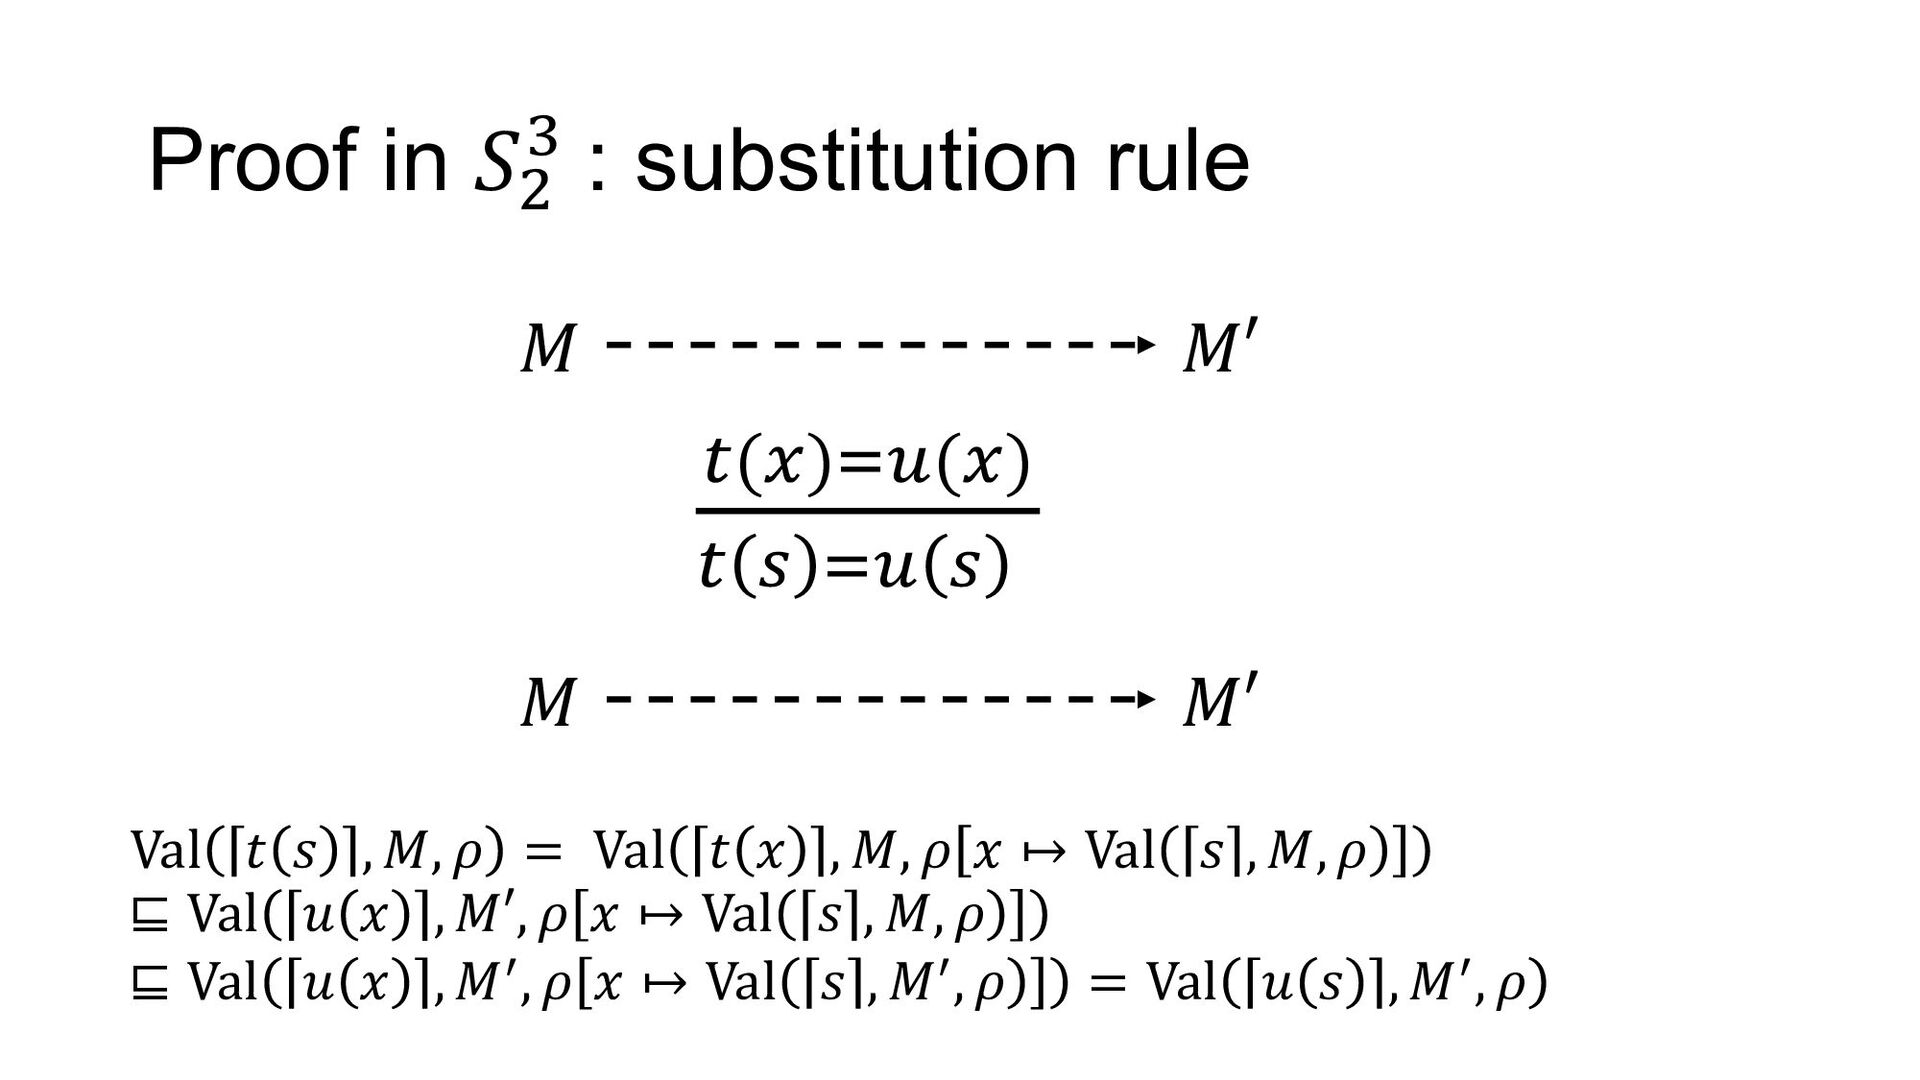
Proof in 𝑆N z : substitution rule !(#)%&(#) ! '
%& ' 𝑀 𝑀′ 𝑀 𝑀′ Val 𝑡 𝑠 , 𝑀, 𝜌 = Val 𝑡 𝑥 , 𝑀, 𝜌 𝑥 ↦ Val 𝑠 , 𝑀, 𝜌 ⊑ Val 𝑢 𝑥 , 𝑀′, 𝜌 𝑥 ↦ Val 𝑠 , 𝑀, 𝜌 ⊑ Val 𝑢 𝑥 , 𝑀C, 𝜌 𝑥 ↦ Val 𝑠 , 𝑀C, 𝜌 = Val 𝑢 𝑠 , 𝑀C, 𝜌 -
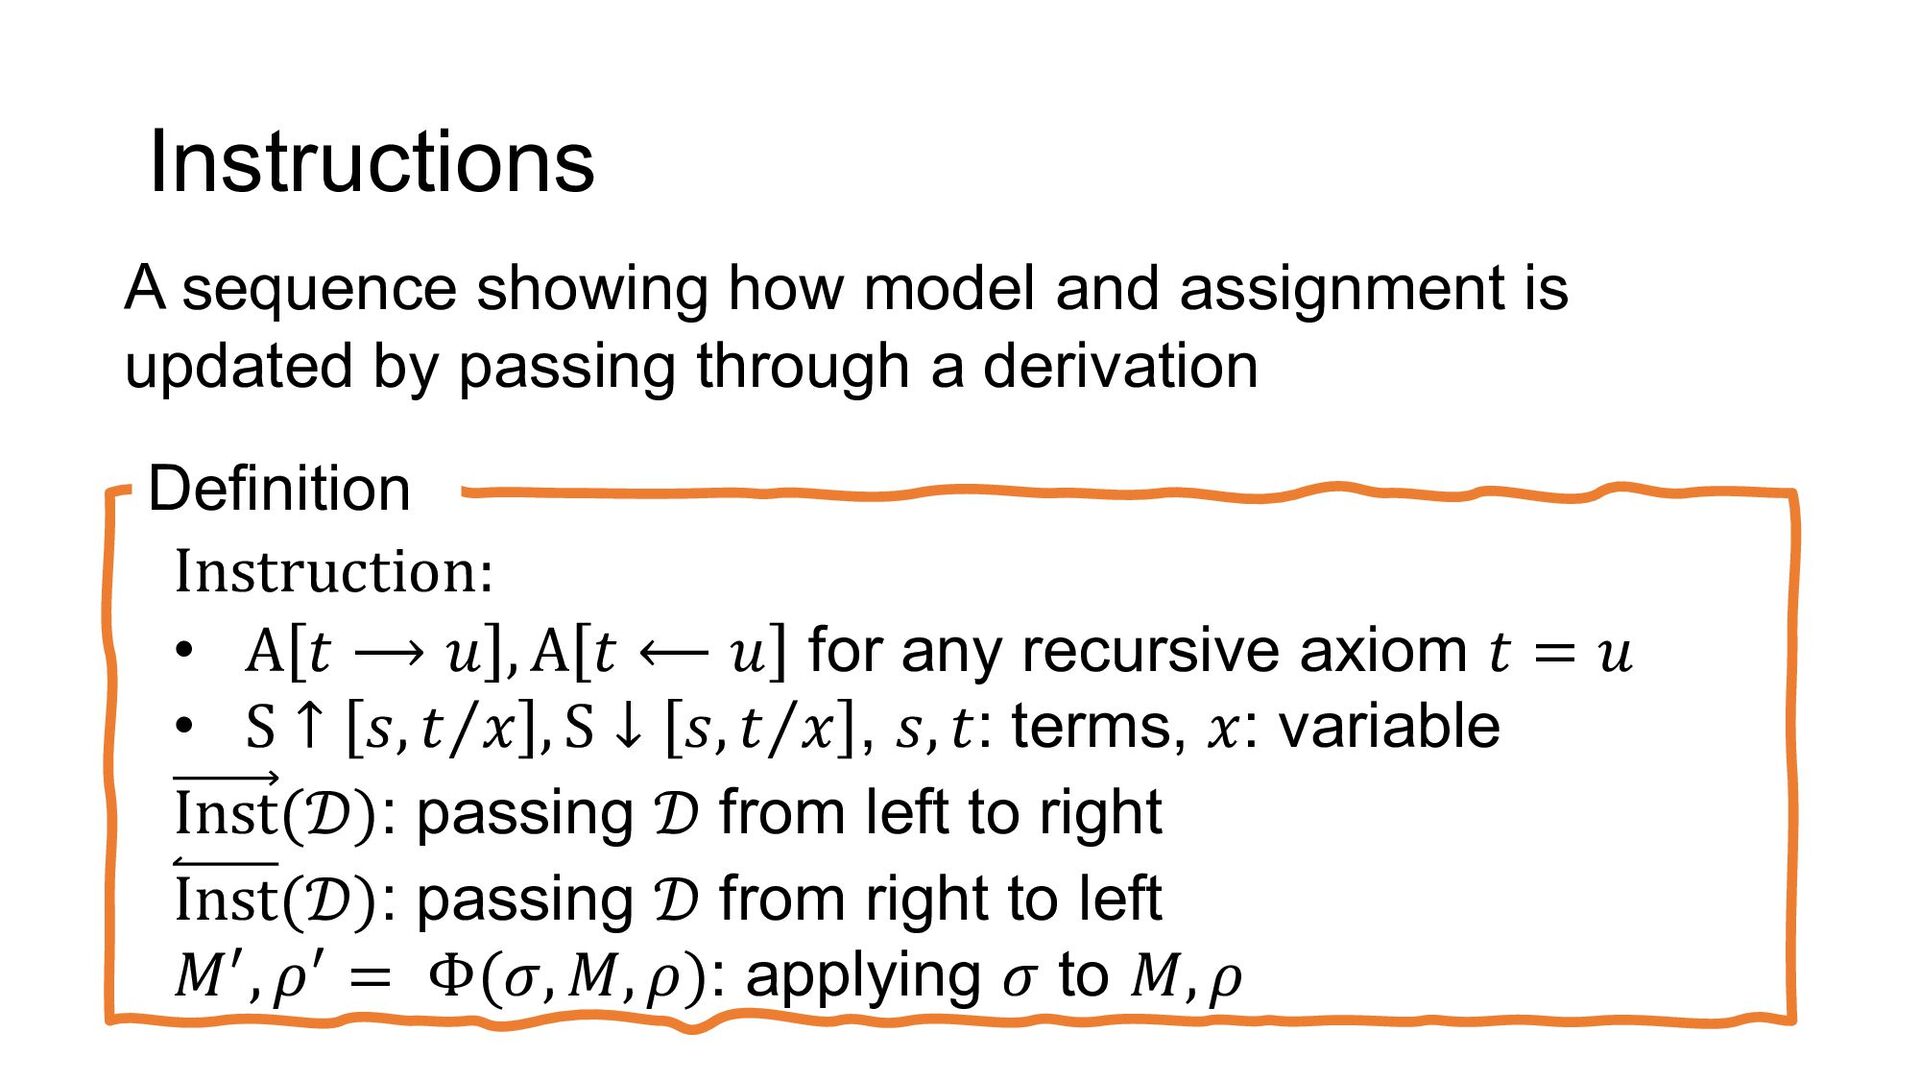
Instructions A sequence showing how model and assignment is updated
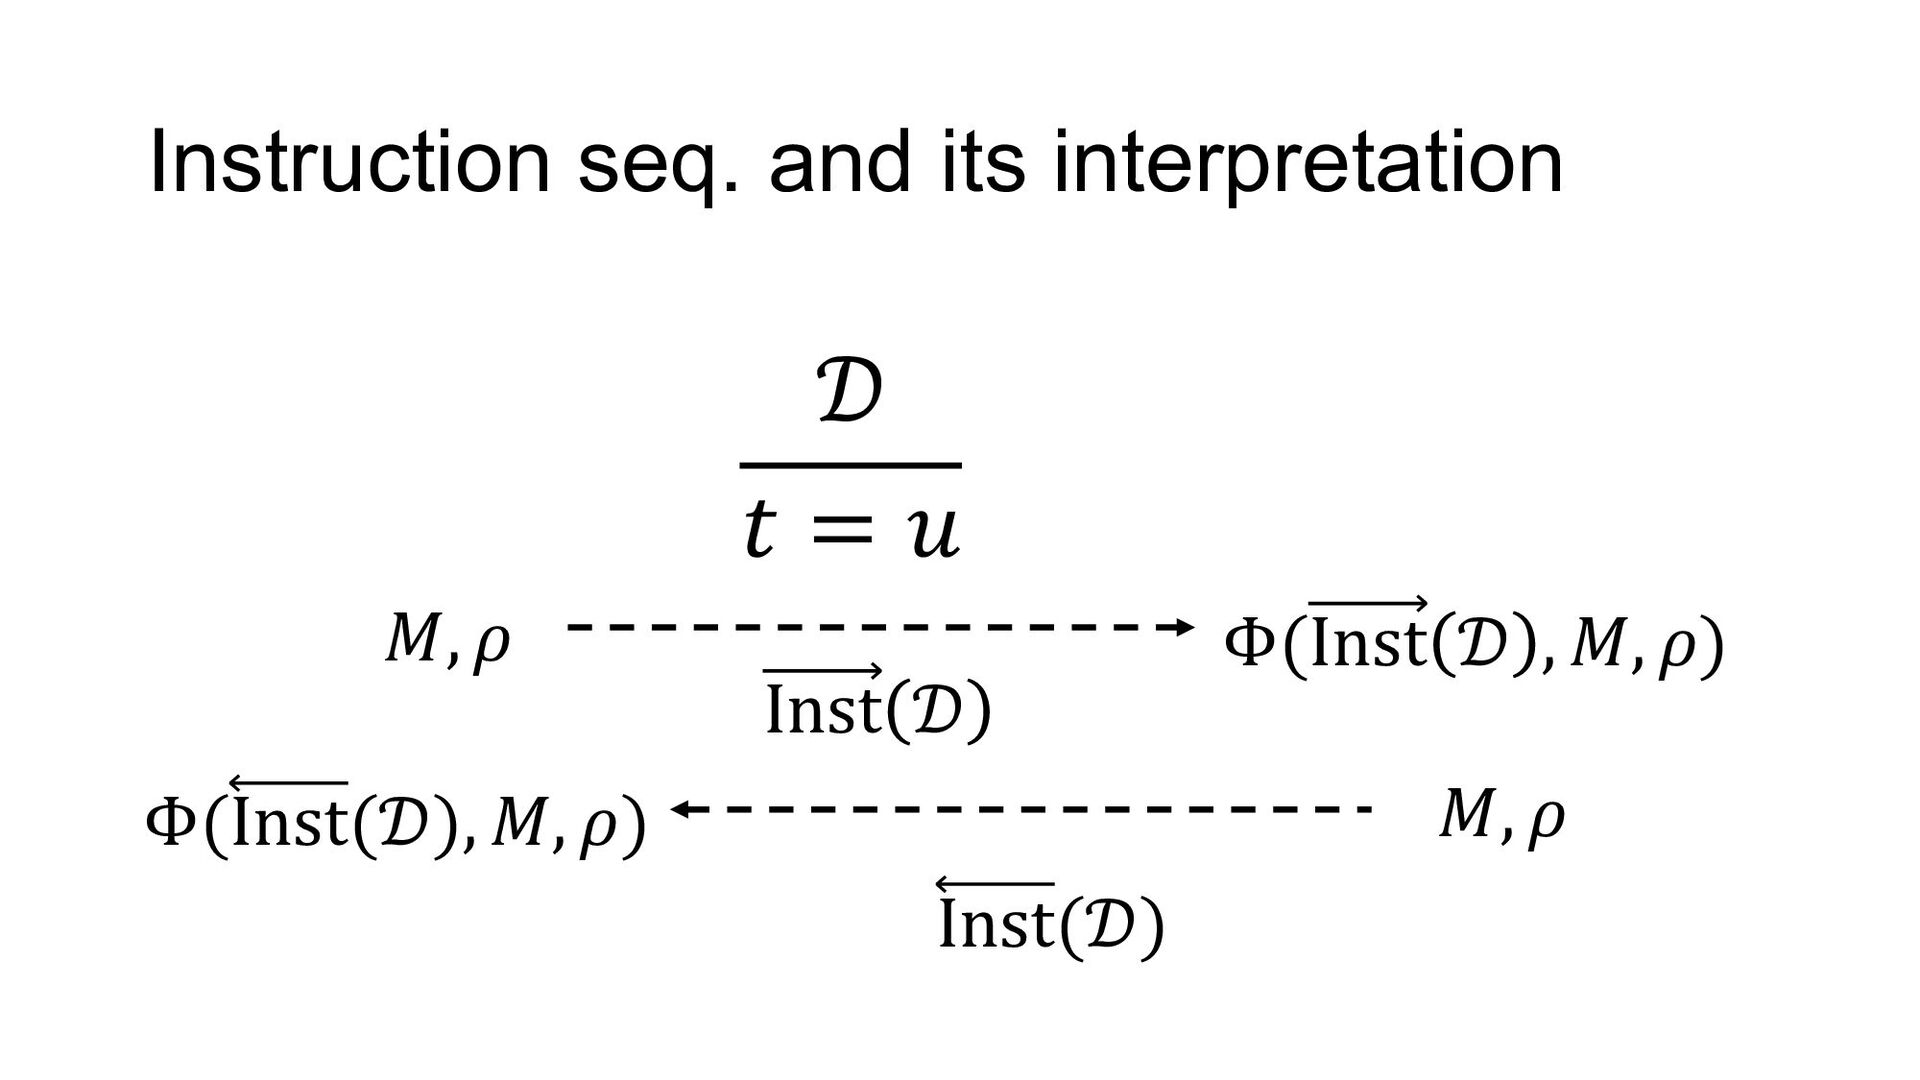
by passing through a derivation Instruction: • A 𝑡 ⟶ 𝑢 , A 𝑡 ⟵ 𝑢 for any recursive axiom 𝑡 = 𝑢 • S ↑ 𝑠, ⁄ 𝑡 𝑥 , S ↓ 𝑠, ⁄ 𝑡 𝑥 , 𝑠, 𝑡: terms, 𝑥: variable Inst(𝒟): passing 𝒟 from left to right Inst(𝒟): passing 𝒟 from right to left 𝑀%, 𝜌% = Φ(𝜎, 𝑀, 𝜌): applying 𝜎 to 𝑀, 𝜌 Definition -
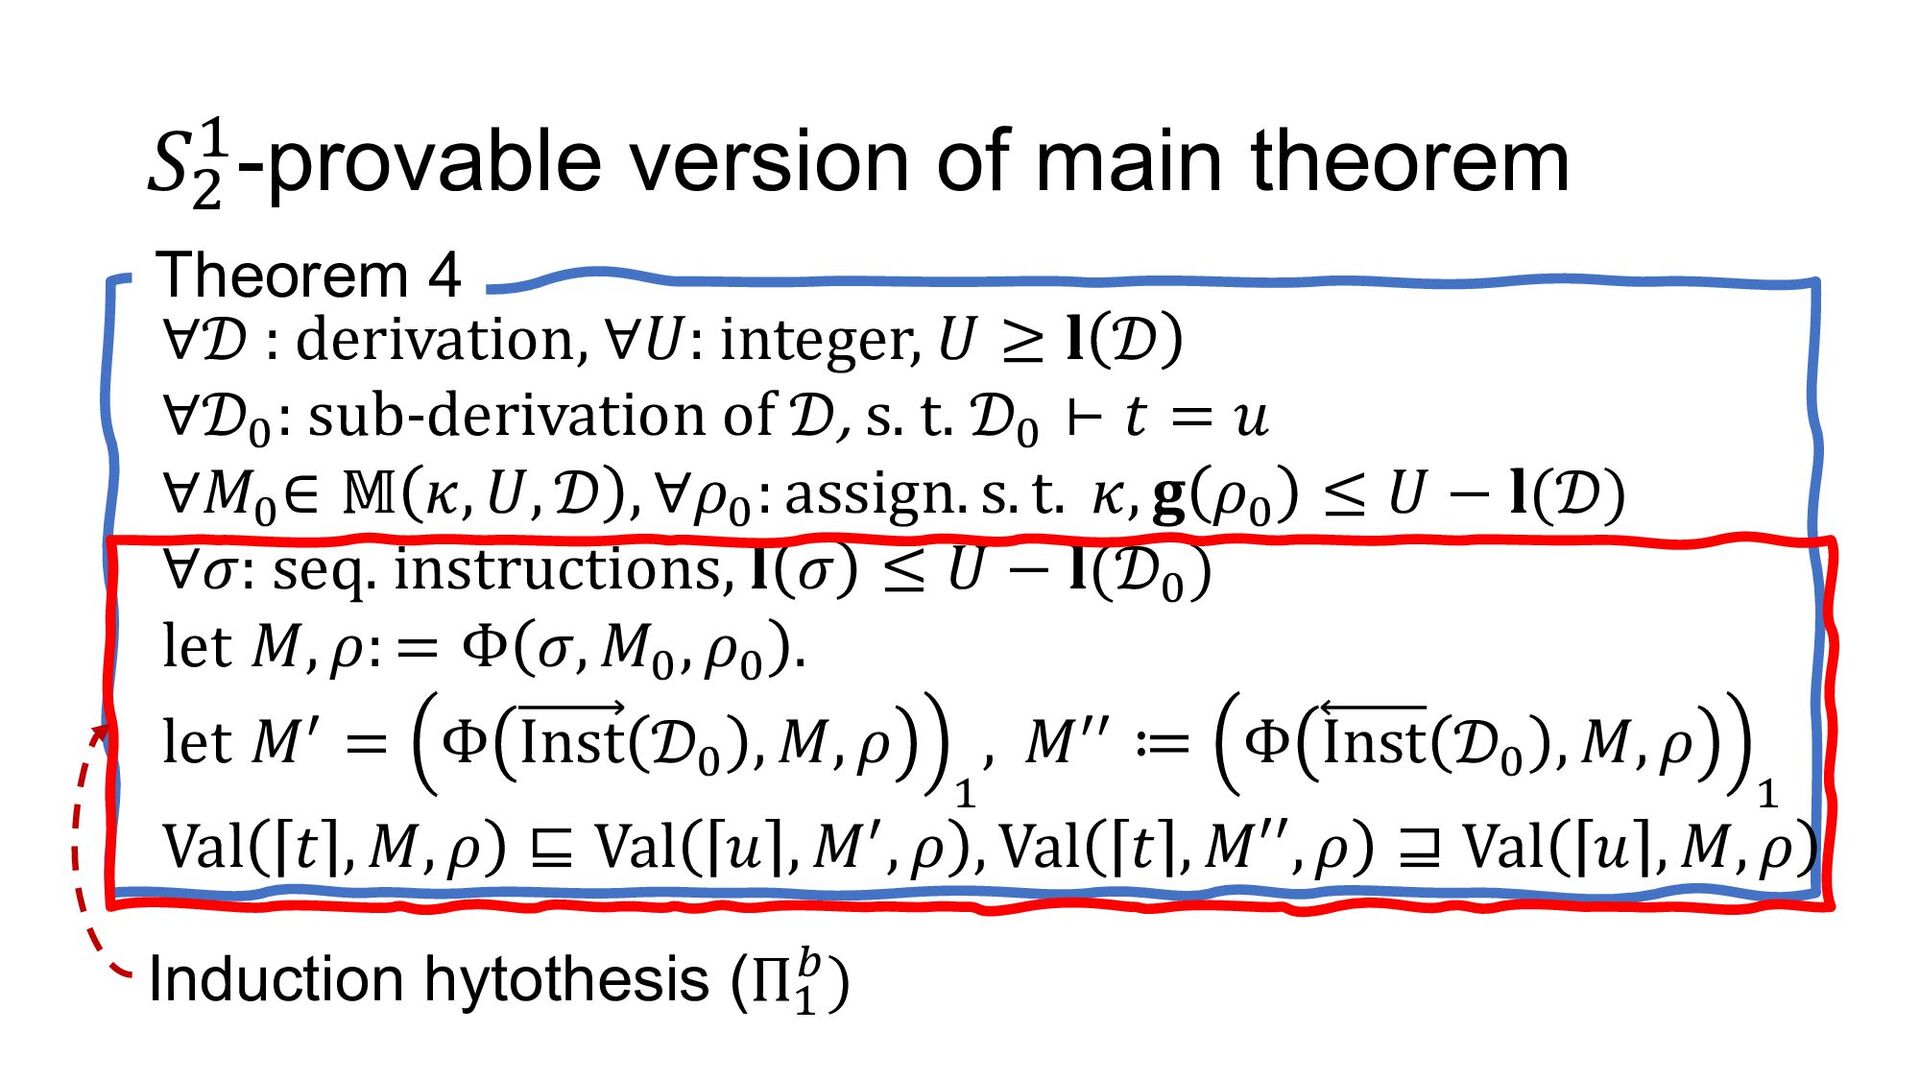
𝑆N O-provable version of main theorem Theorem 4 ∀𝒟 :
derivation, ∀𝑈: integer, 𝑈 ≥ 𝐥 𝒟 ∀𝒟' : sub-derivation of 𝒟, s. t. 𝒟' ⊢ 𝑡 = 𝑢 ∀𝑀' ∈ 𝕄 𝜅, 𝑈, 𝒟 , ∀𝜌' : assign. s. t. 𝜅, 𝐠 𝜌' ≤ 𝑈 − 𝐥(𝒟) ∀𝜎: seq. instructions, 𝐥 𝜎 ≤ 𝑈 − 𝐥(𝒟' ) let 𝑀, 𝜌: = Φ 𝜎, 𝑀' , 𝜌' . let 𝑀% = Φ Inst 𝒟' , 𝑀, 𝜌 $ , 𝑀%% ≔ Φ Inst 𝒟' , 𝑀, 𝜌 $ Val 𝑡 , 𝑀, 𝜌 ⊑ Val 𝑢 , 𝑀%, 𝜌 , Val 𝑡 , 𝑀′′, 𝜌 ⊒ Val 𝑢 , 𝑀, 𝜌 Induction hytothesis (Π$ () -
Instruction seq. and its interpretation 𝒟 𝑡 = 𝑢 Inst
𝒟 Inst(𝒟) 𝑀, 𝜌 Φ(Inst 𝒟 , 𝑀, 𝜌) 𝑀, 𝜌 Φ(Inst(𝒟), 𝑀, 𝜌) -
Instruction seq. for a derivation ⊢ 𝑓(𝑡) = 𝑢 A[𝑓(𝑡)
→ 𝑢] A[𝑓(𝑡) ← 𝑢] 𝑀, 𝜌 𝑀, 𝜌 𝑀, 𝜌 𝑀% ) ≔ 𝑀 𝑓 ∪ {𝑣 ↦ 𝑀 𝑔 𝑣, 𝑀 𝑓 𝑣 } where 𝑣 = 𝜌(𝑥) 𝑀′, 𝜌 -
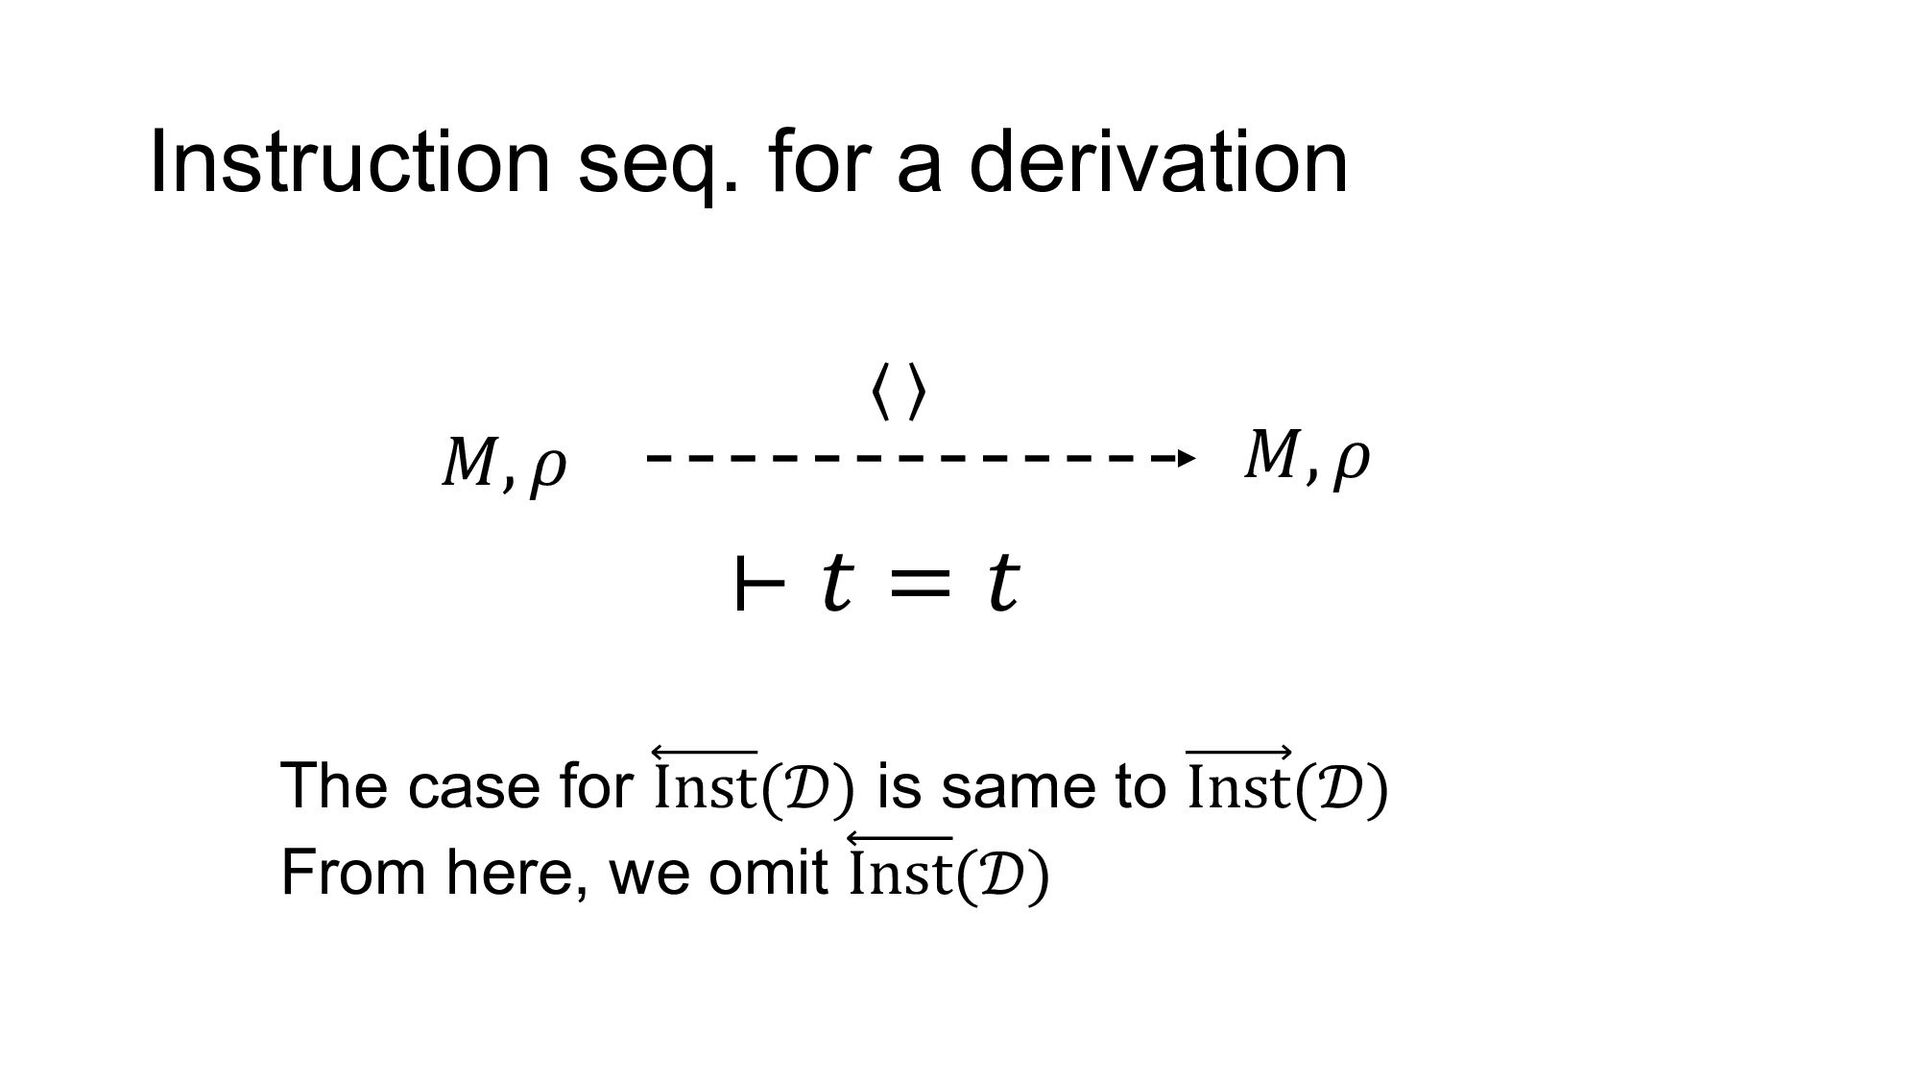
⊢ 𝑡 = 𝑡 𝑀, 𝜌 𝑀, 𝜌 The case
for Inst(𝒟) is same to Inst(𝒟) From here, we omit Inst(𝒟) Instruction seq. for a derivation -
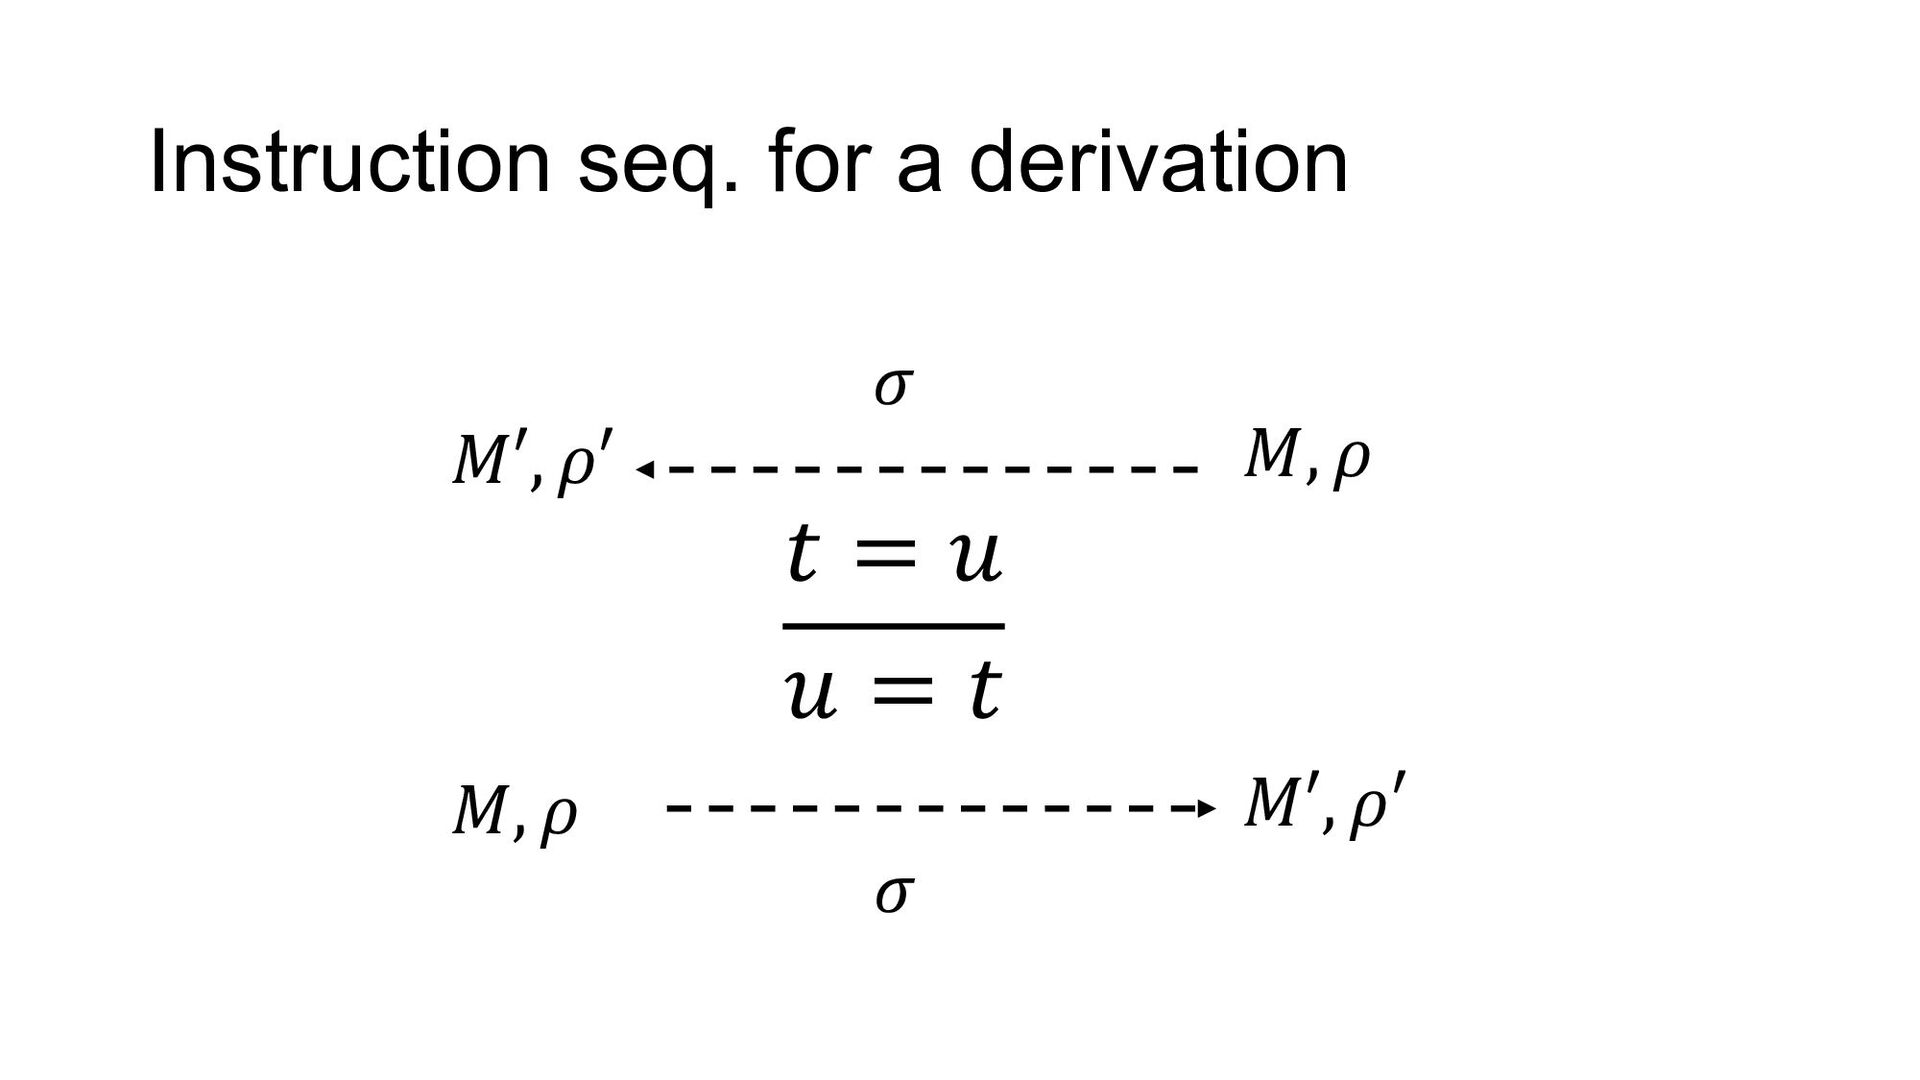
𝑡 = 𝑢 𝑢 = 𝑡 𝑀′, 𝜌′ 𝑀, 𝜌
𝜎 𝑀, 𝜌 𝑀′, 𝜌′ 𝜎 Instruction seq. for a derivation -
𝑡 = 𝑢 𝑢 = 𝑠 𝑢 = 𝑠 𝑀,
𝜌 𝑀! , 𝜌! 𝑀" , 𝜌" 𝜎$ 𝜎! 𝑀, 𝜌 𝑀" , 𝜌" 𝜎! ∷ 𝜎" Instruction seq. for a derivation -
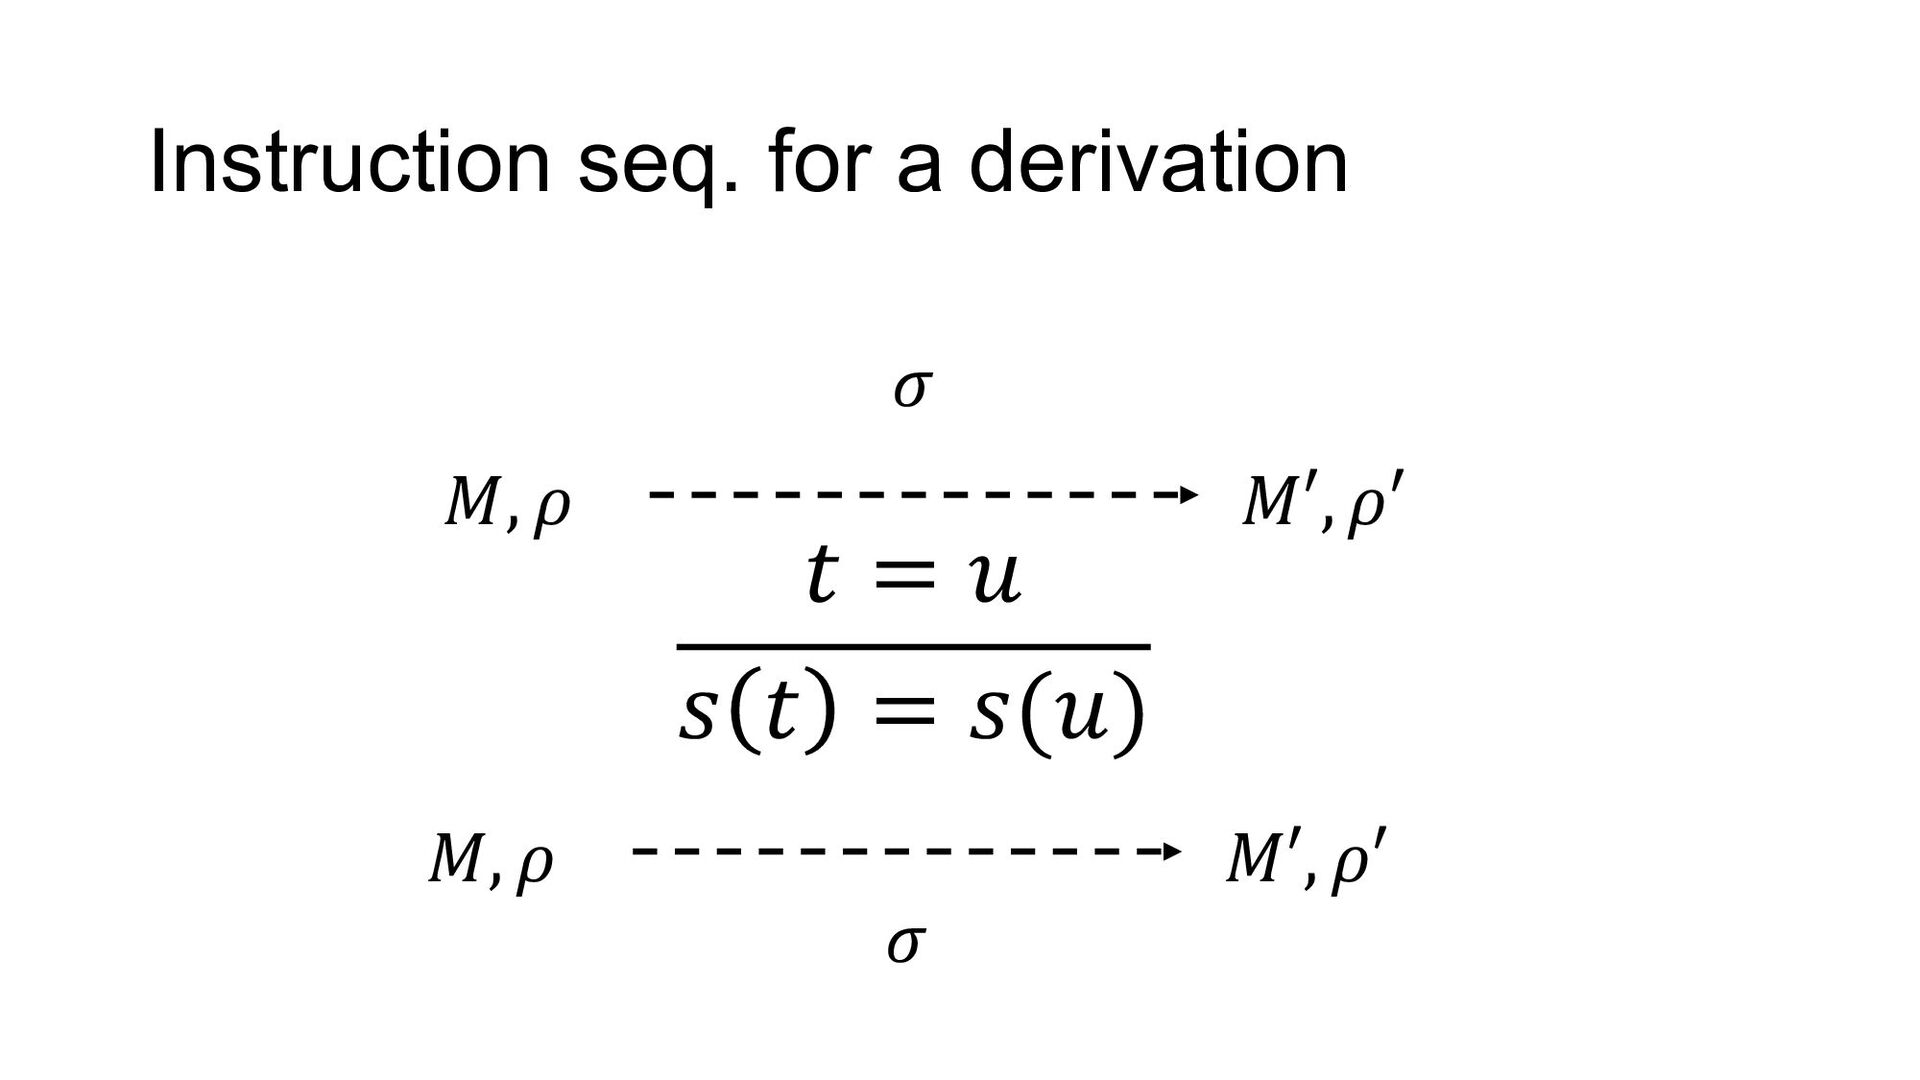
𝑡 = 𝑢 𝑠 𝑡 = 𝑠(𝑢) 𝑀, 𝜌 𝑀′,
𝜌′ 𝜎 𝑀, 𝜌 𝑀′, 𝜌′ 𝜎 Instruction seq. for a derivation -
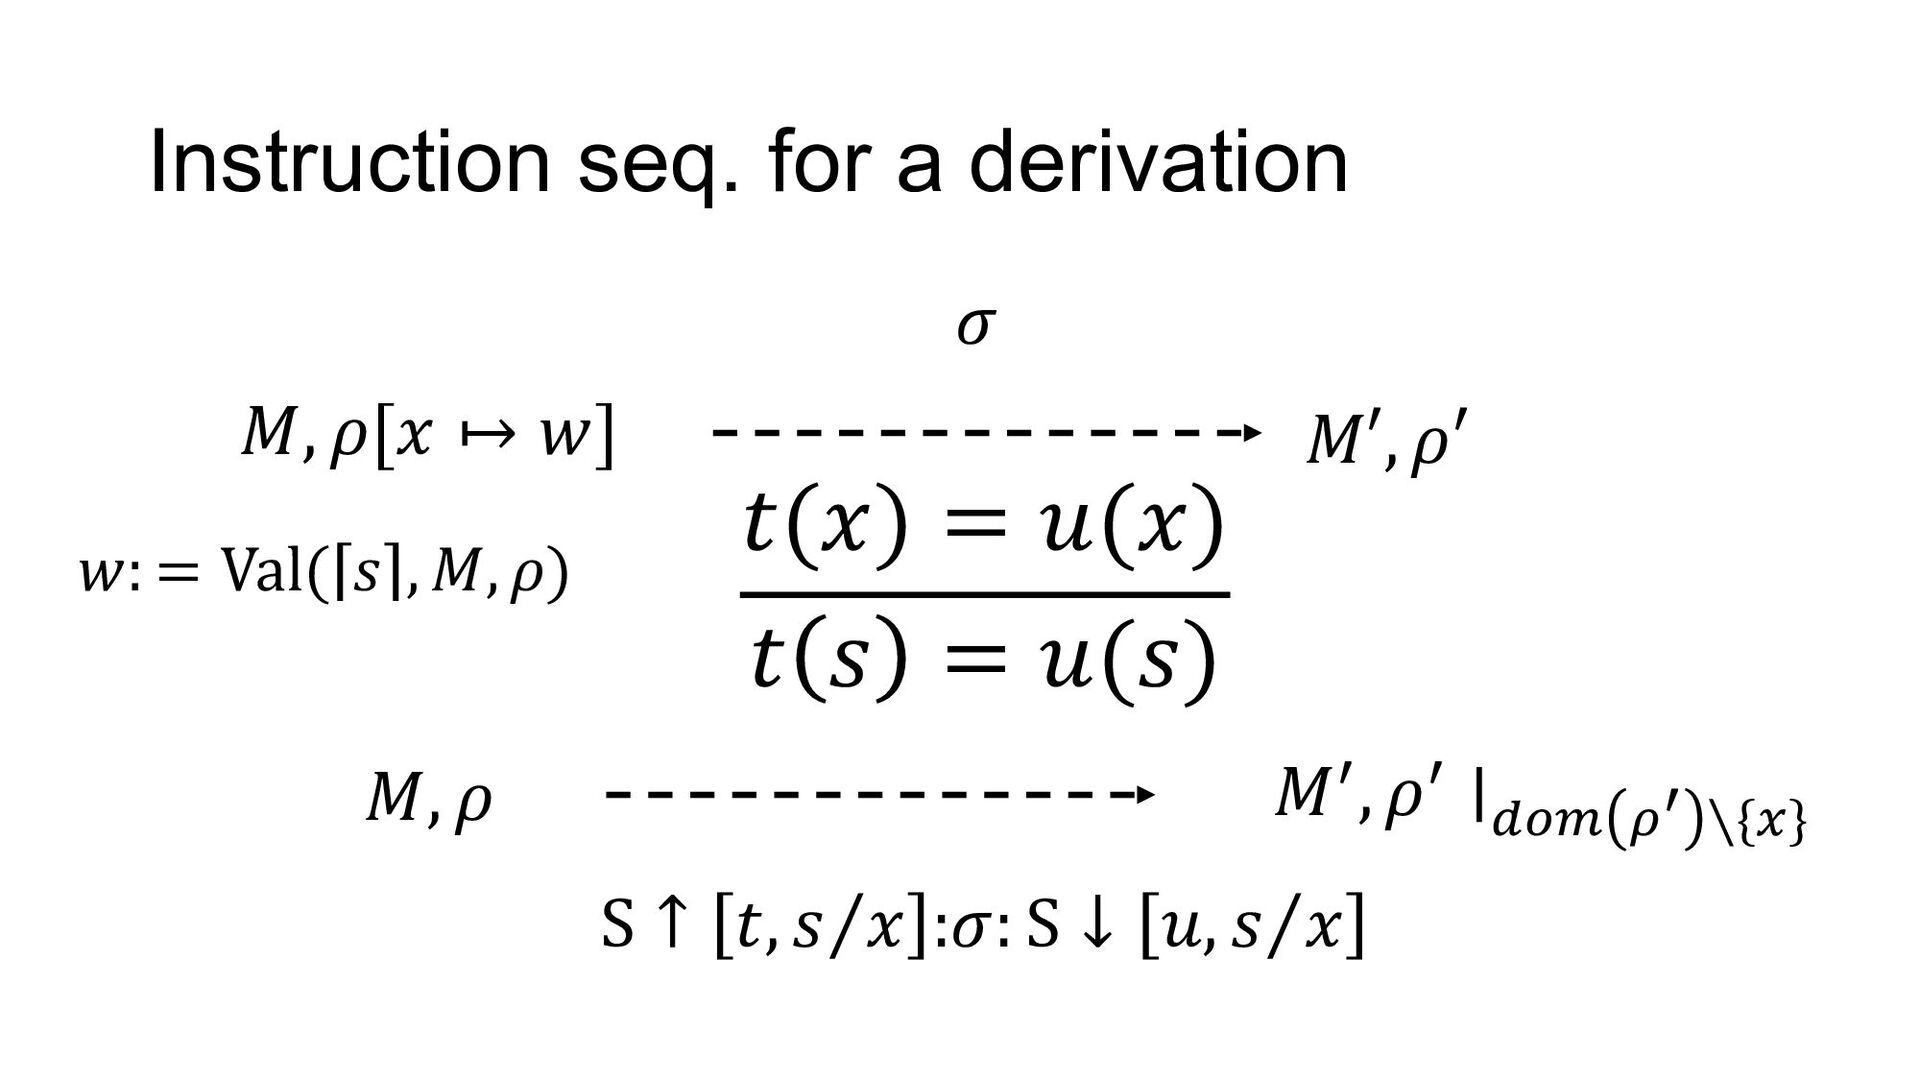
𝑡(𝑥) = 𝑢(𝑥) 𝑡 𝑠 = 𝑢(𝑠) 𝑀, 𝜌[𝑥 ↦
𝑤] 𝑀′, 𝜌′ 𝜎 𝑀, 𝜌 𝑀#, 𝜌# ∣$%& '! ∖{*} S ↑ 𝑡, ⁄ 𝑠 𝑥 :𝜎: S ↓ 𝑢, ⁄ 𝑠 𝑥 Instruction seq. for a derivation 𝑤: = Val( 𝑠 , 𝑀, 𝜌) -
Main lemma 𝑀 ∈ 𝕄 𝜅, 𝑈, 𝒟 , 𝜌:
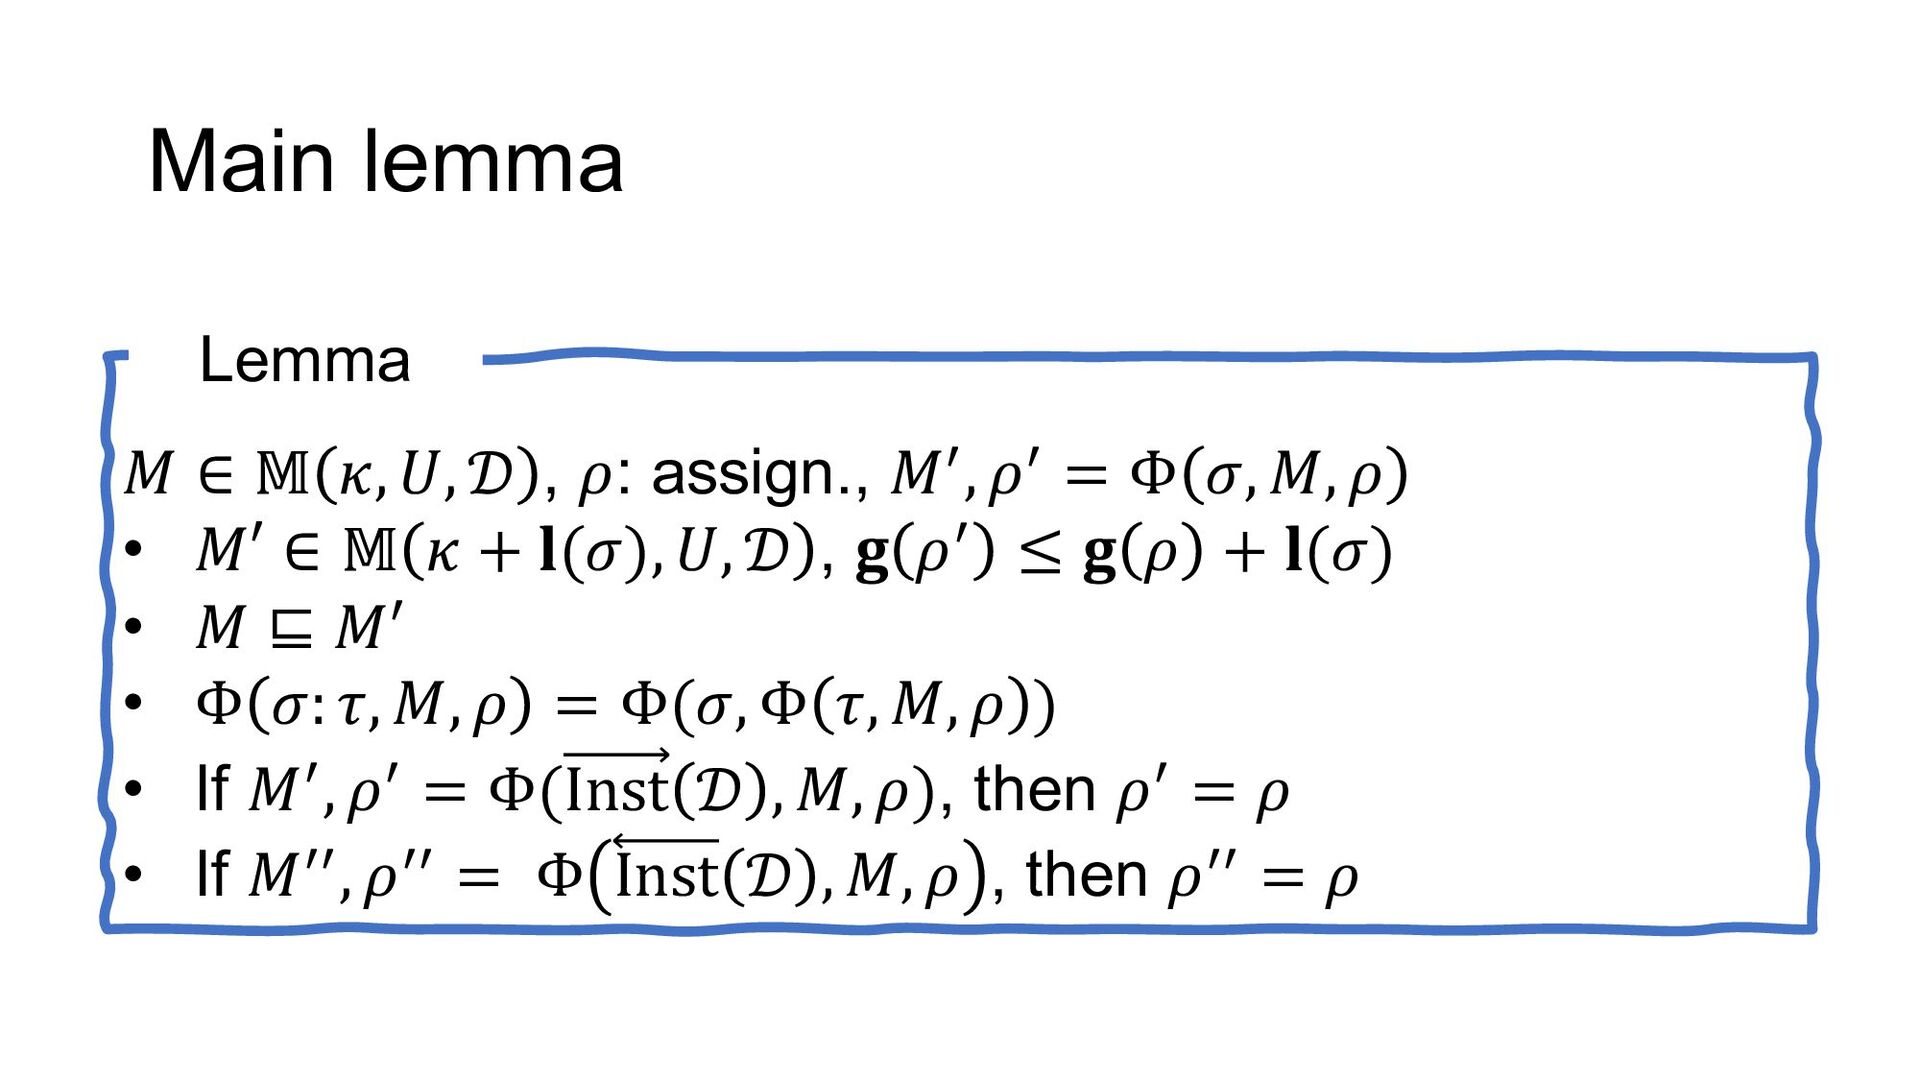
assign., 𝑀%, 𝜌% = Φ 𝜎, 𝑀, 𝜌 • 𝑀′ ∈ 𝕄 𝜅 + 𝐥(𝜎), 𝑈, 𝒟 , 𝐠 𝜌% ≤ 𝐠 𝜌 + 𝐥(𝜎) • 𝑀 ⊑ 𝑀% • Φ 𝜎: 𝜏, 𝑀, 𝜌 = Φ(𝜎, Φ 𝜏, 𝑀, 𝜌 ) • If 𝑀%, 𝜌% = Φ(Inst 𝒟 , 𝑀, 𝜌), then 𝜌% = 𝜌 • If 𝑀%%, 𝜌%% = Φ Inst 𝒟 , 𝑀, 𝜌 , then 𝜌%% = 𝜌 Lemma -
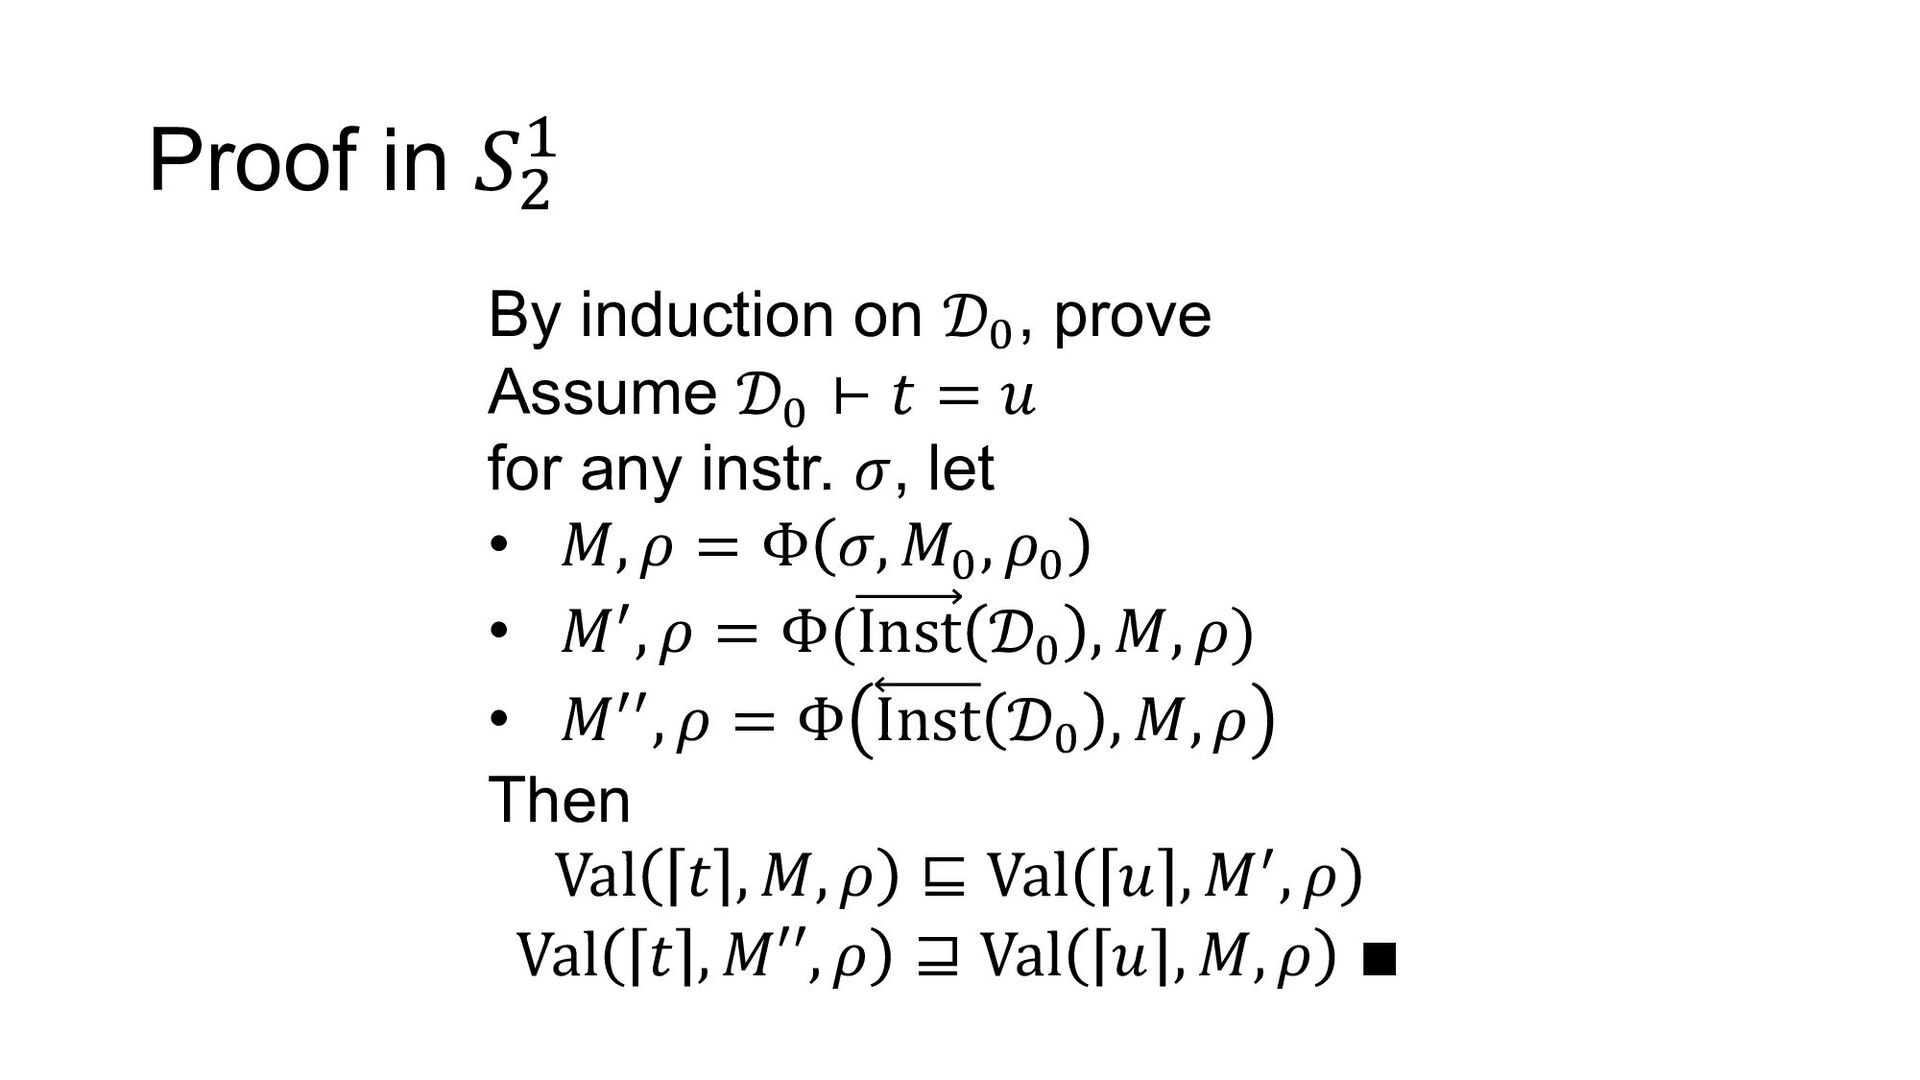
Proof in 𝑆N O By induction on 𝒟' , prove
Assume 𝒟' ⊢ 𝑡 = 𝑢 for any instr. 𝜎, let • 𝑀, 𝜌 = Φ 𝜎, 𝑀' , 𝜌' • 𝑀%, 𝜌 = Φ(Inst 𝒟' , 𝑀, 𝜌) • 𝑀%%, 𝜌 = Φ Inst 𝒟' , 𝑀, 𝜌 Then Val 𝑡 , 𝑀, 𝜌 ⊑ Val 𝑢 , 𝑀%, 𝜌 Val 𝑡 , 𝑀′′, 𝜌 ⊒ Val 𝑢 , 𝑀, 𝜌 ∎