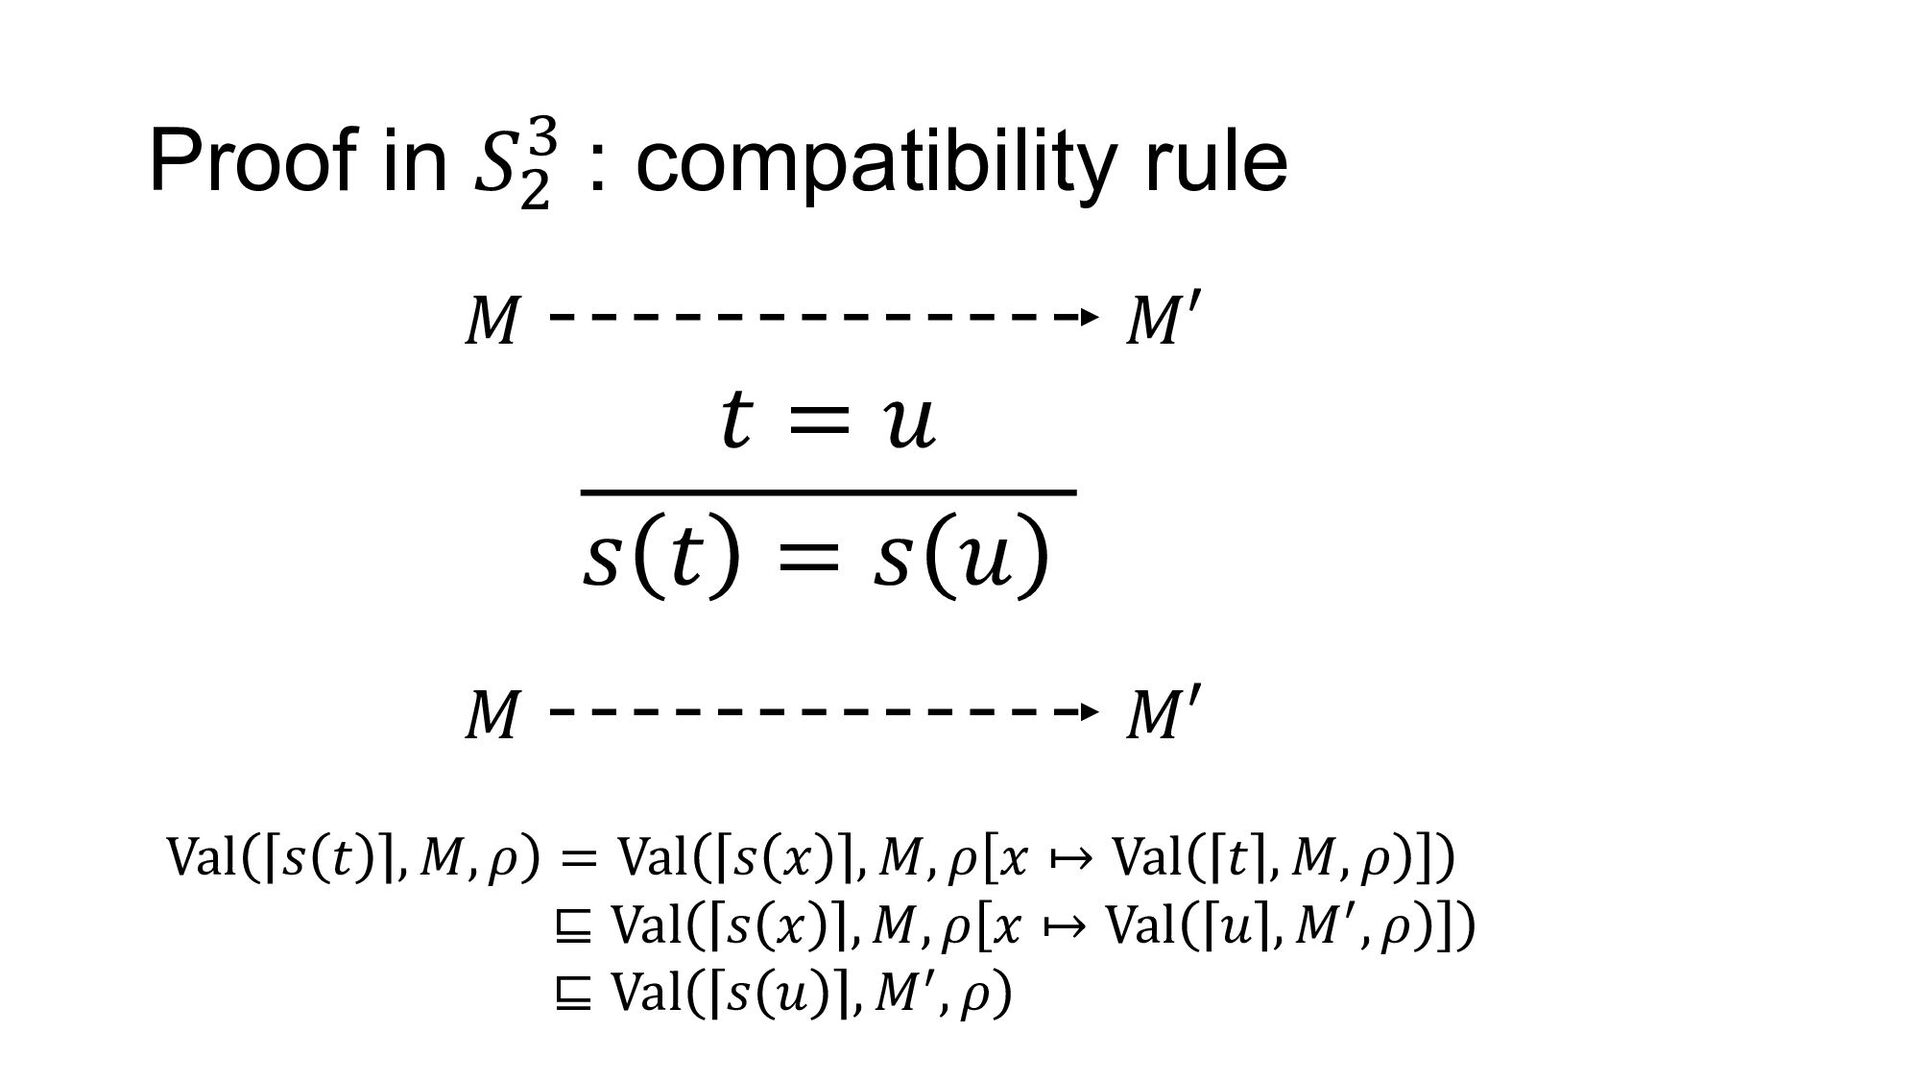Upgrade to Pro — share decks privately, control downloads, hide ads and more …

On proving consistency of equational theories i...

On proving consistency of equational theories in bounded arithmetic

Yoriyuki Yamagata

October 16, 2022

Transcript

49 slides
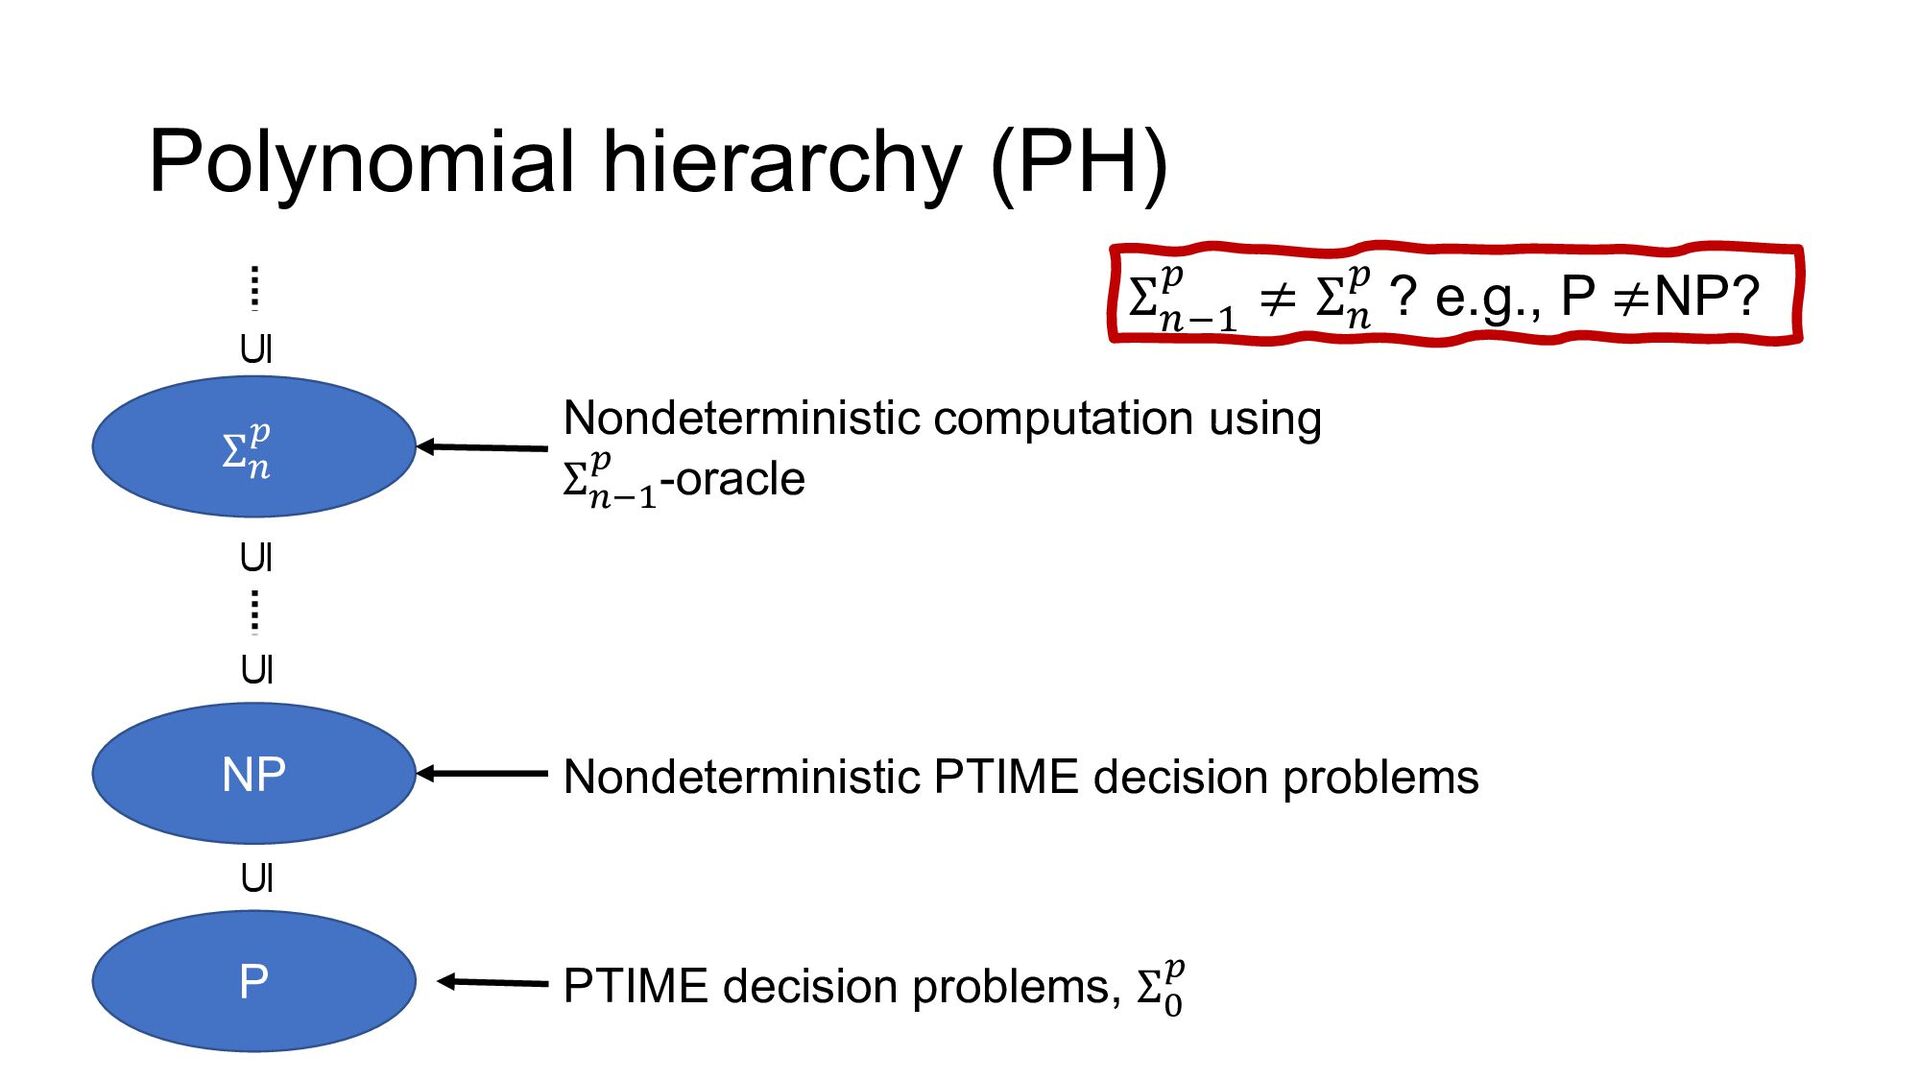
  1. Polynomial hierarchy (PH) P NP Σ! " ⊆ ⊆ ⊆

    ⊆ PTIME decision problems, Σ# " Nondeterministic PTIME decision problems Nondeterministic computation using Σ!$% " -oracle Σ!"# $ ≠ Σ! $ ? e.g., P ≠NP?
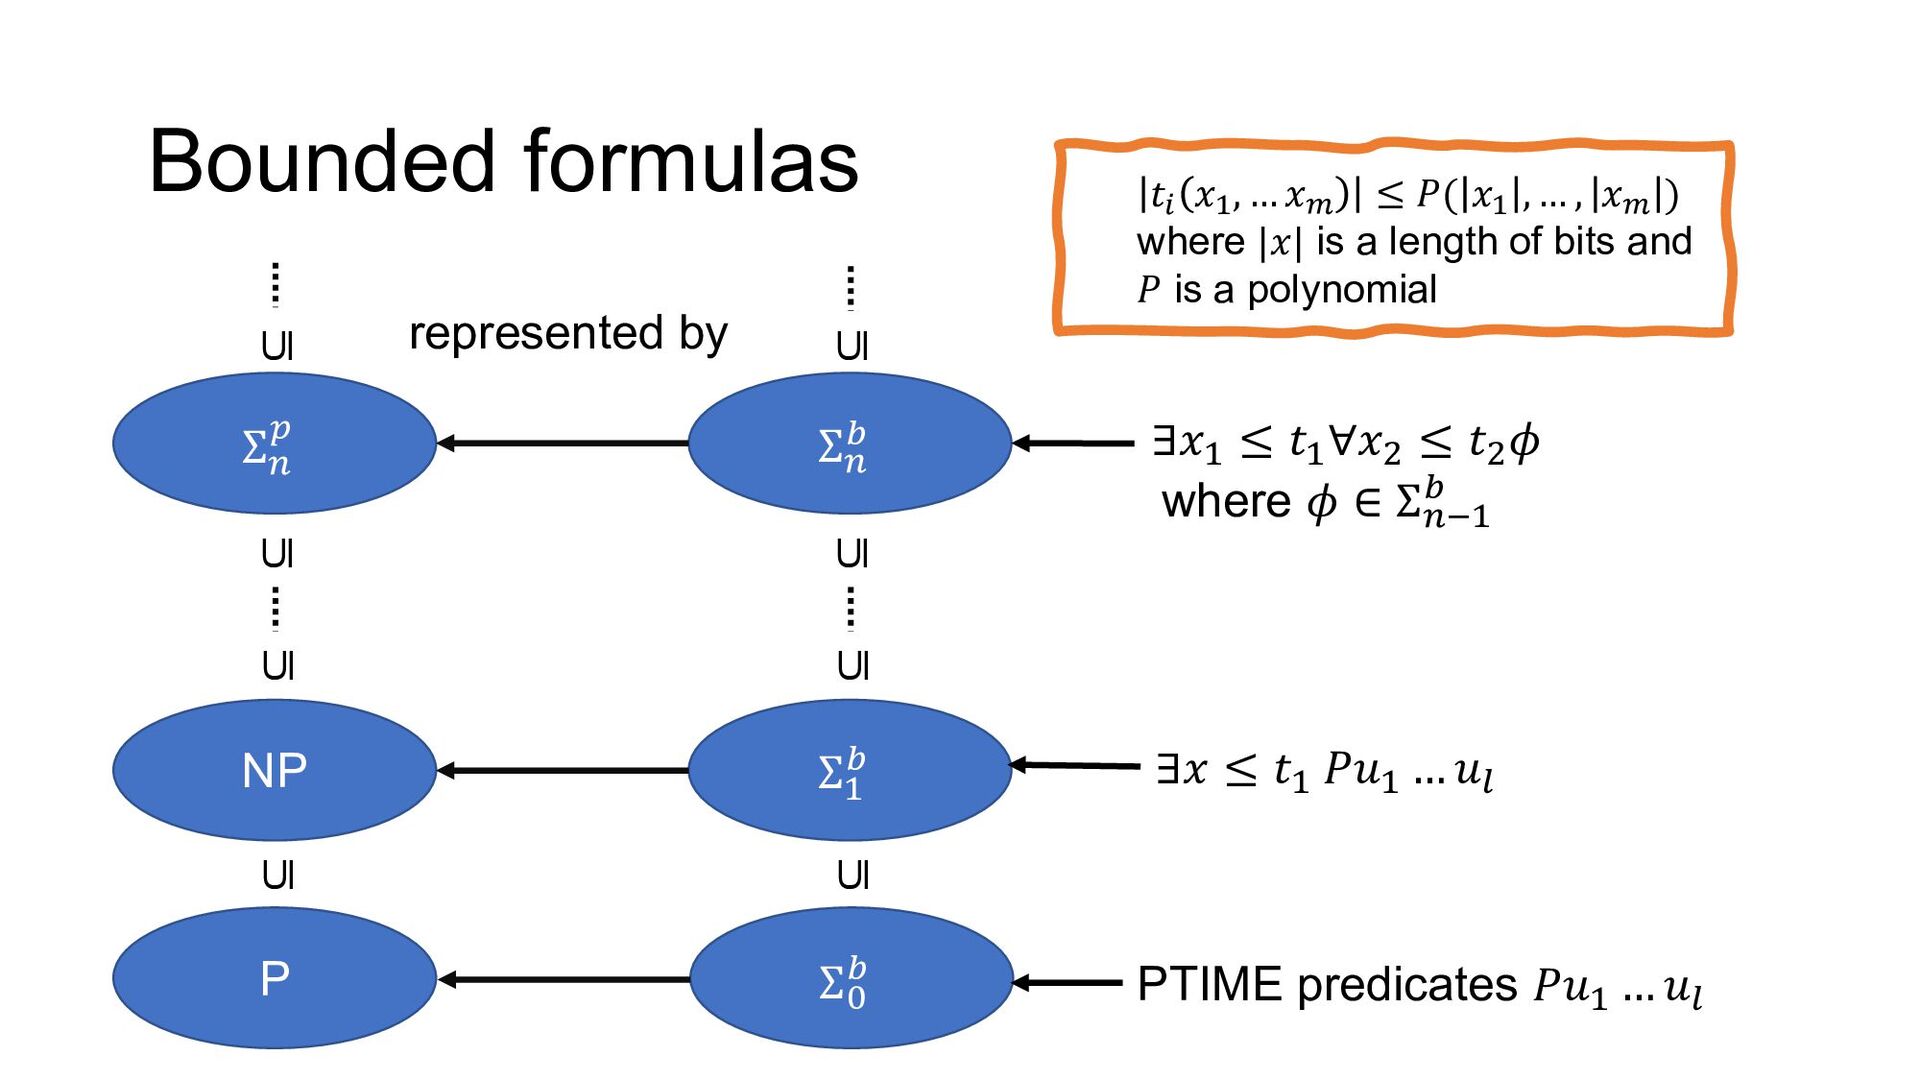
  2. Bounded formulas ∃𝑥% ≤ 𝑡%∀𝑥& ≤ 𝑡&𝜙 where 𝜙 ∈

    Σ!$% ' Σ# ' Σ% ' Σ! ' ⊆ ⊆ ⊆ ⊆ PTIME predicates 𝑃𝑢% … 𝑢( ∃𝑥 ≤ 𝑡% 𝑃𝑢% … 𝑢( P NP Σ! " ⊆ ⊆ ⊆ ⊆ represented by 𝑡! 𝑥", … 𝑥# ≤ 𝑃( 𝑥" , … , 𝑥# ) where |𝑥| is a length of bits and 𝑃 is a polynomial
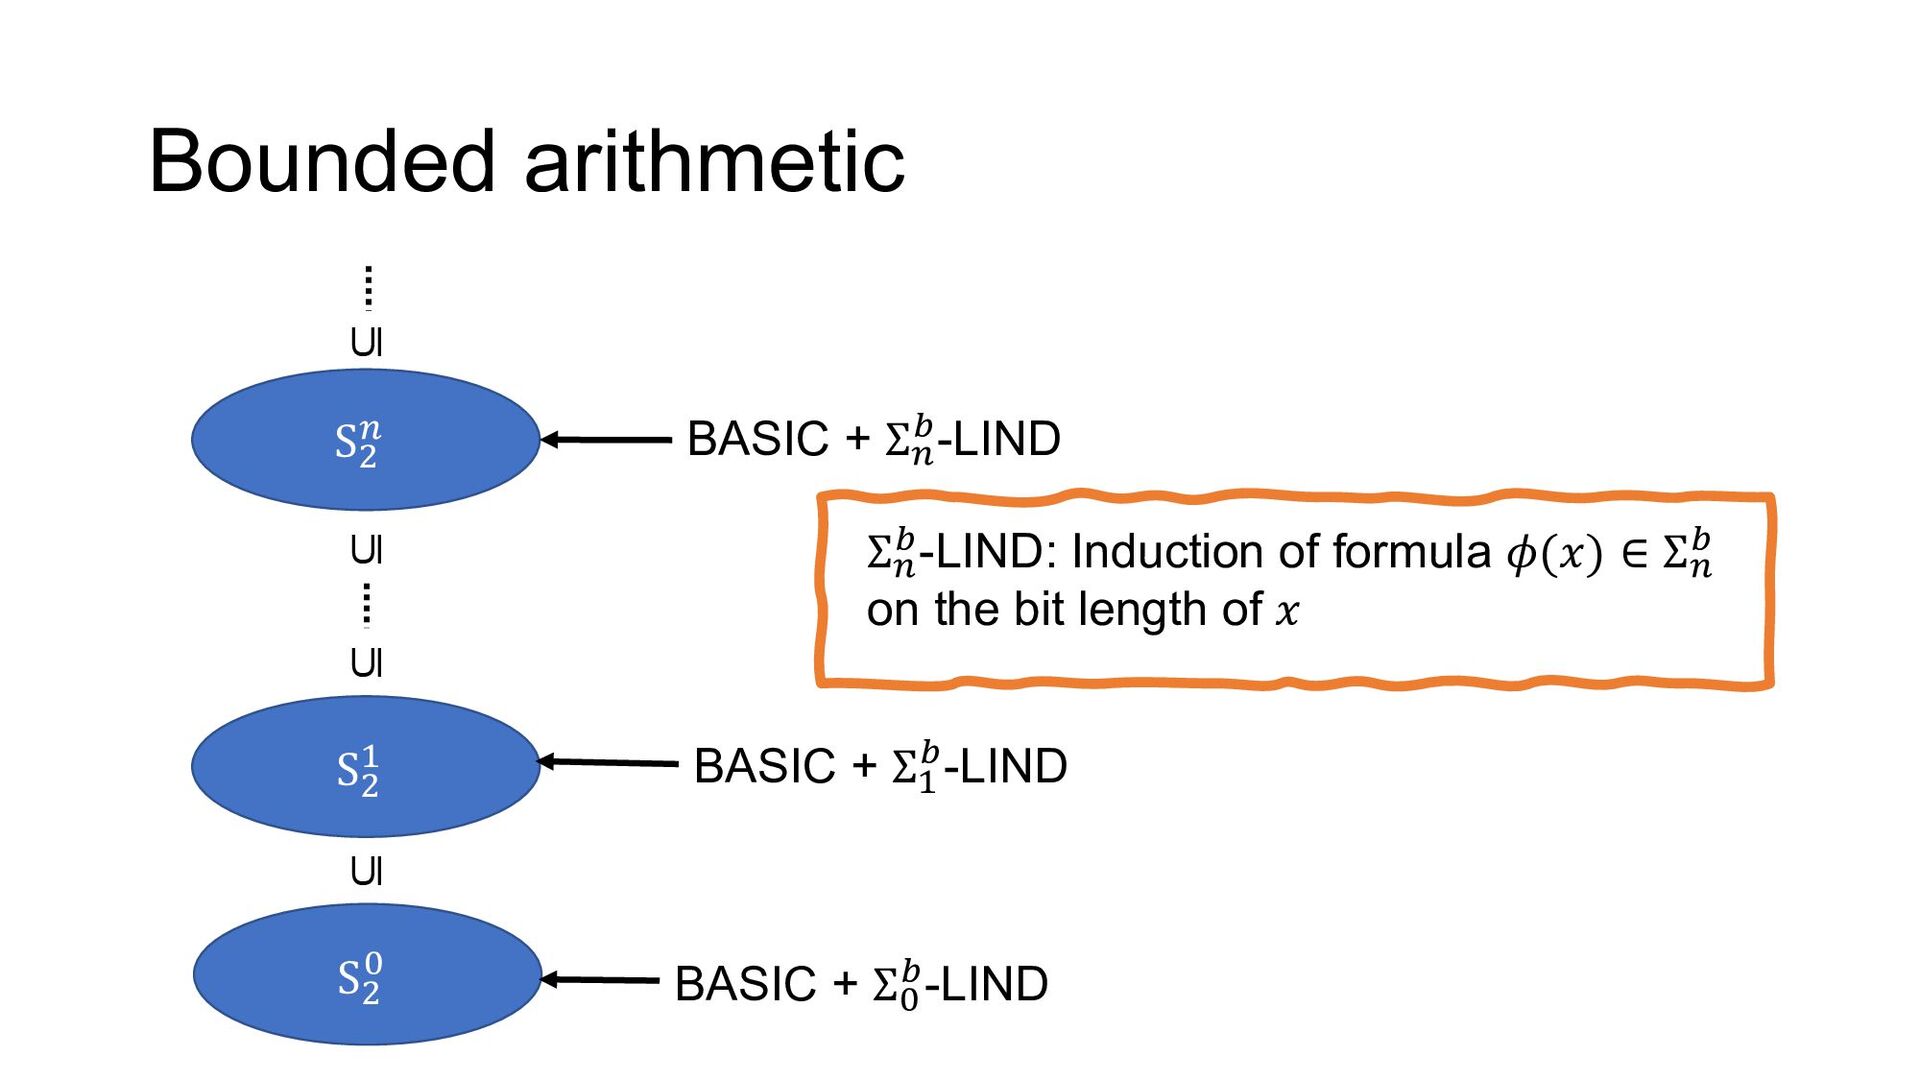
  3. Bounded arithmetic BASIC + Σ! '-LIND S& # S& %

    S& ! ⊆ ⊆ ⊆ ⊆ BASIC + Σ# '-LIND BASIC + Σ% '-LIND Σ! '-LIND: Induction of formula 𝜙(𝑥) ∈ Σ! ' on the bit length of 𝑥
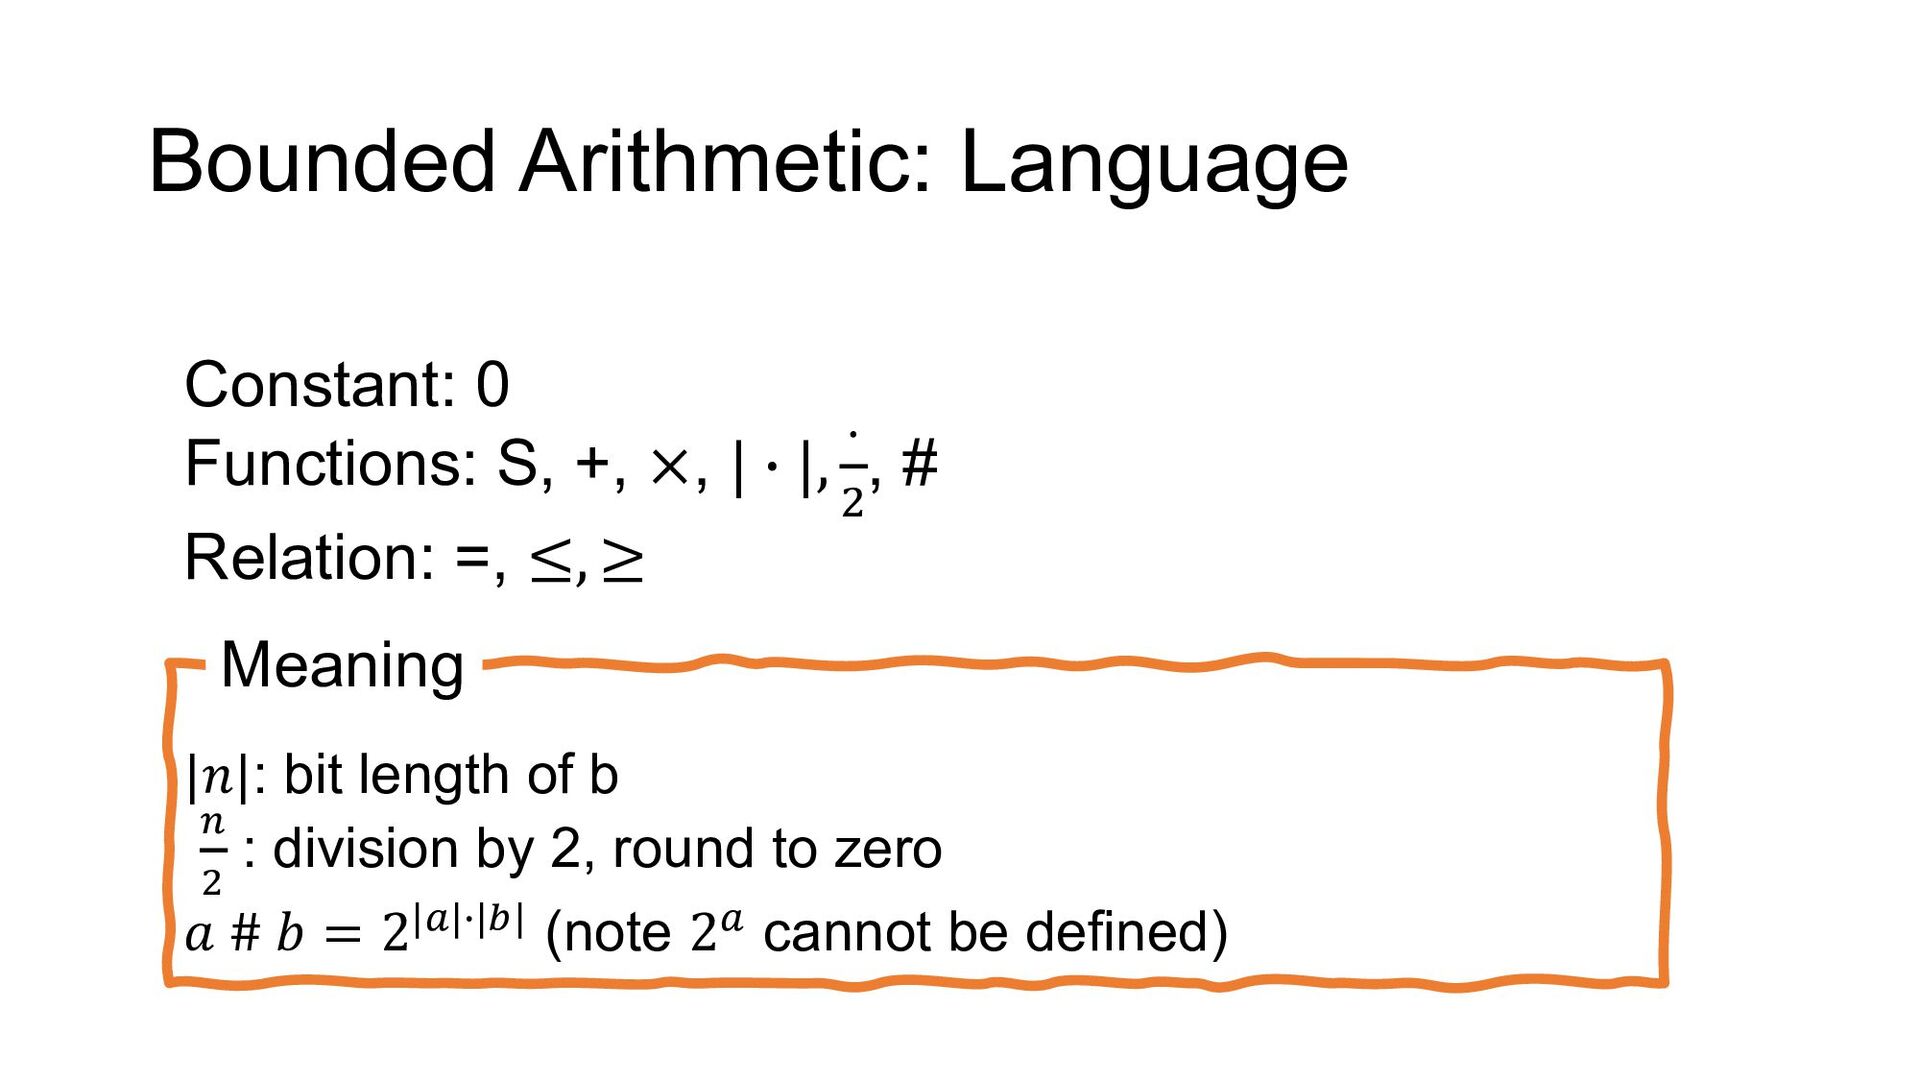
  4. Bounded Arithmetic: Language Constant: 0 Functions: S, +, ×, |

    # |, ! " , # Relation: =, ≤, ≥ |𝑛|: bit length of b ! . : division by 2, round to zero 𝑎 # 𝑏 = 2|/|0|1| (note 2/ cannot be defined) Meaning
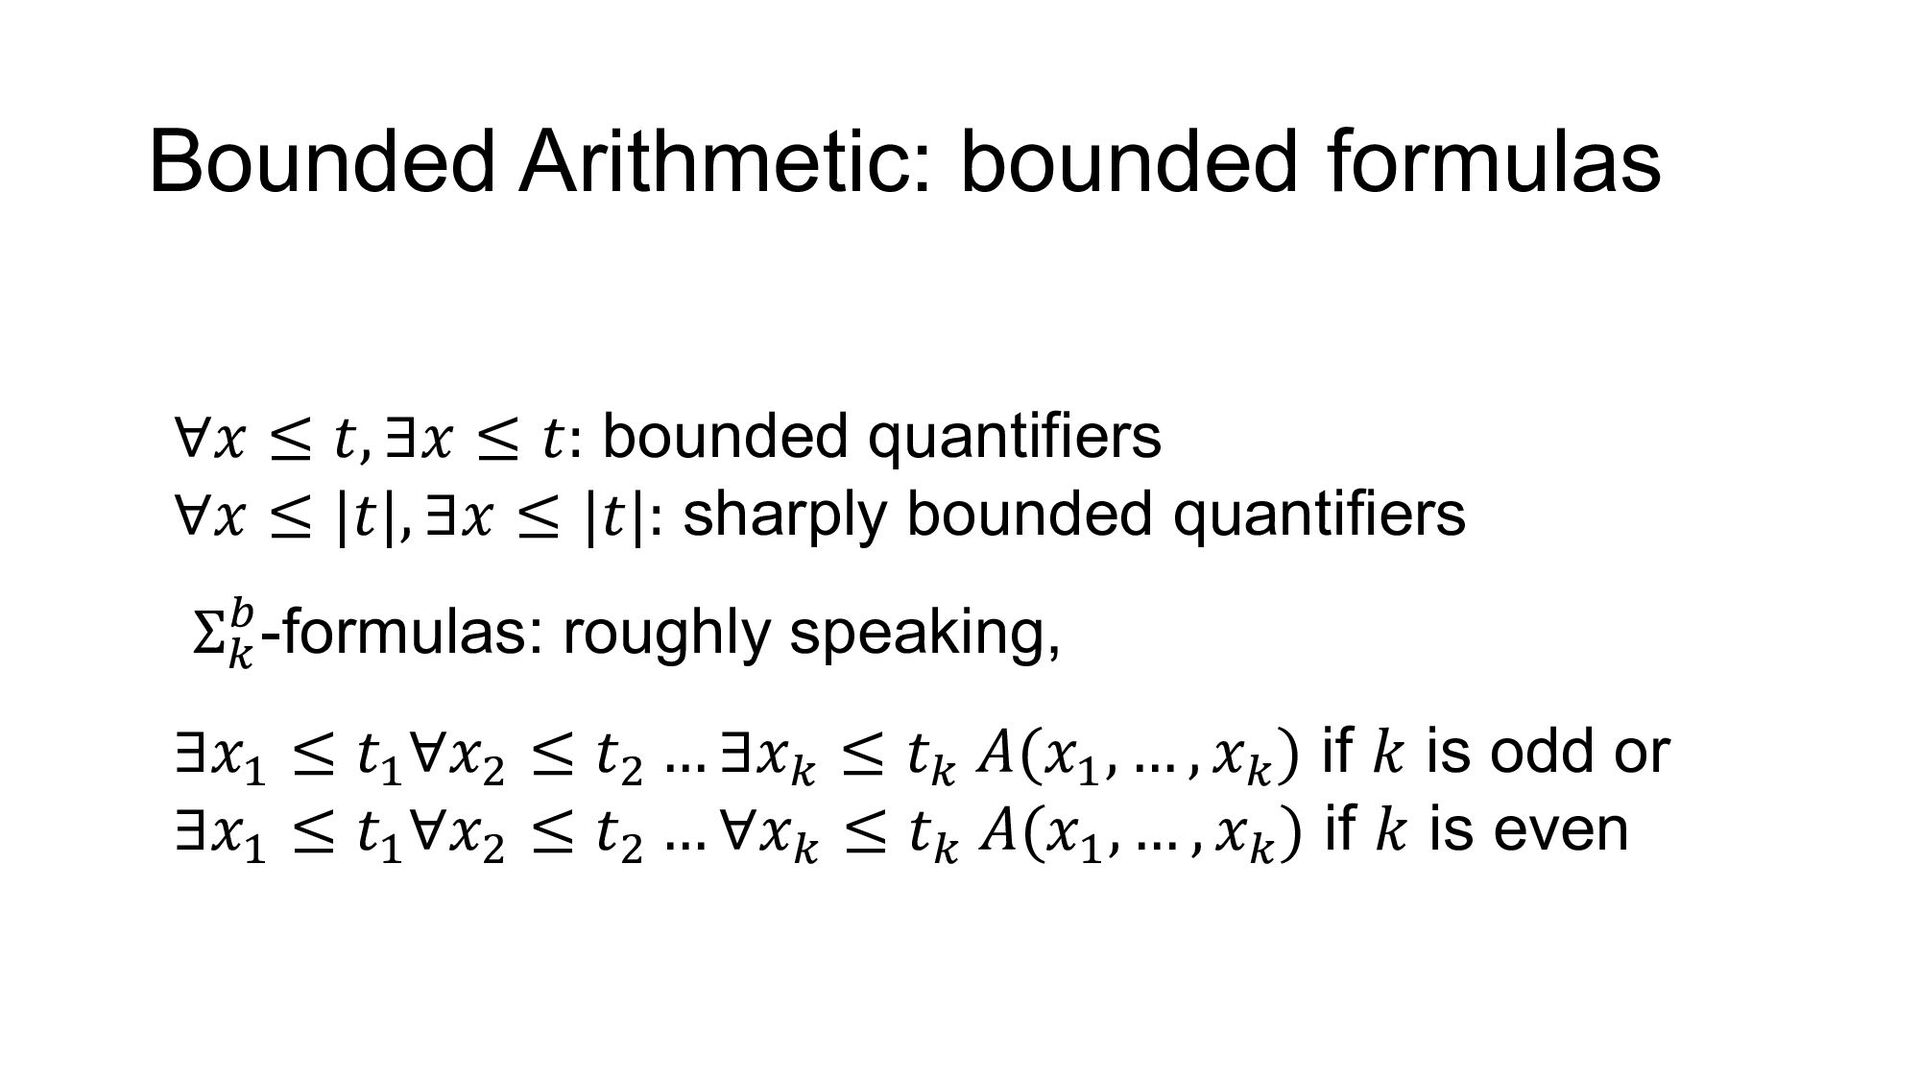
  5. Bounded Arithmetic: bounded formulas ∀𝑥 ≤ 𝑡, ∃𝑥 ≤ 𝑡:

    bounded quantifiers ∀𝑥 ≤ |𝑡|, ∃𝑥 ≤ |𝑡|: sharply bounded quantifiers ∃𝑥# ≤ 𝑡# ∀𝑥" ≤ 𝑡" … ∃𝑥$ ≤ 𝑡$ 𝐴(𝑥# , … , 𝑥$ ) if 𝑘 is odd or ∃𝑥# ≤ 𝑡# ∀𝑥" ≤ 𝑡" … ∀𝑥$ ≤ 𝑡$ 𝐴(𝑥# , … , 𝑥$ ) if 𝑘 is even Σ$ %-formulas: roughly speaking,
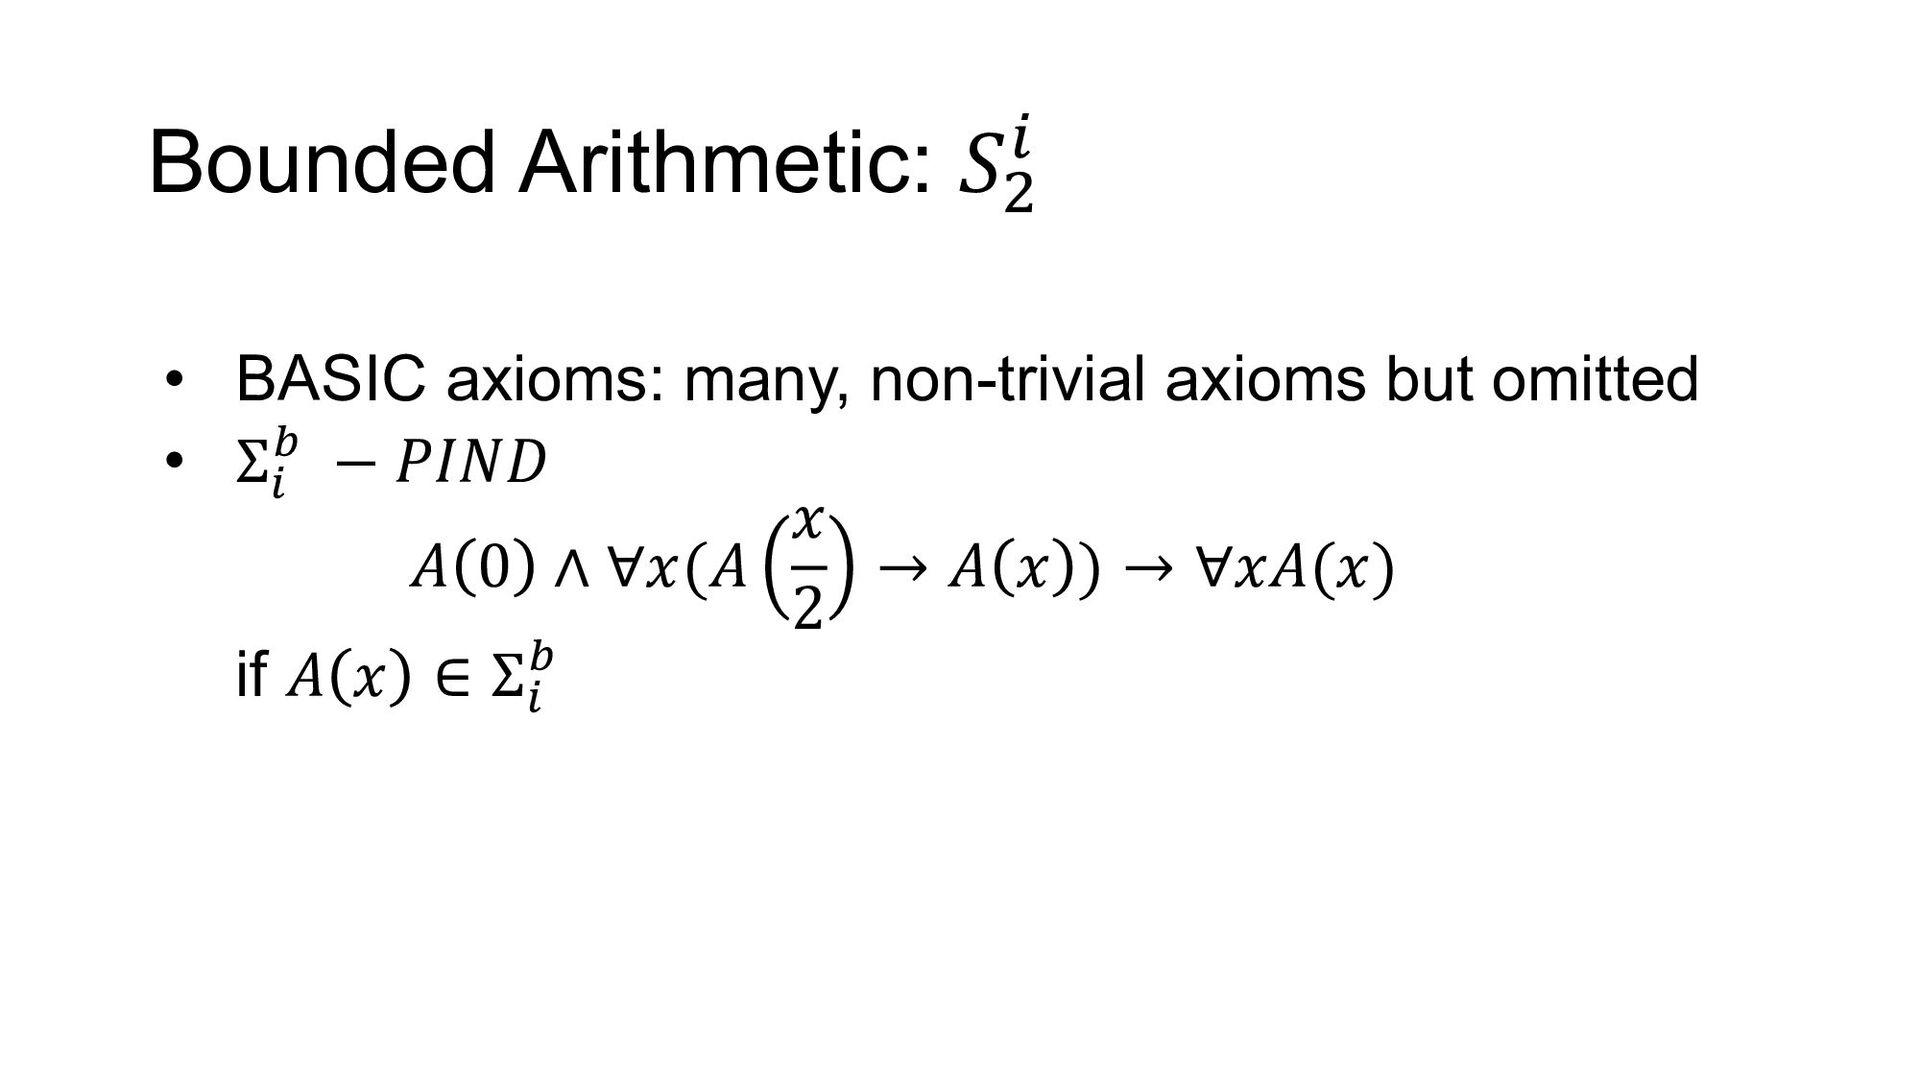
  6. Bounded Arithmetic: 𝑆2 3 • BASIC axioms: many, non-trivial axioms

    but omitted • Σ& % − 𝑃𝐼𝑁𝐷 𝐴 0 ∧ ∀𝑥(𝐴 𝑥 2 → 𝐴 𝑥 ) → ∀𝑥𝐴(𝑥) if 𝐴 𝑥 ∈ Σ& %
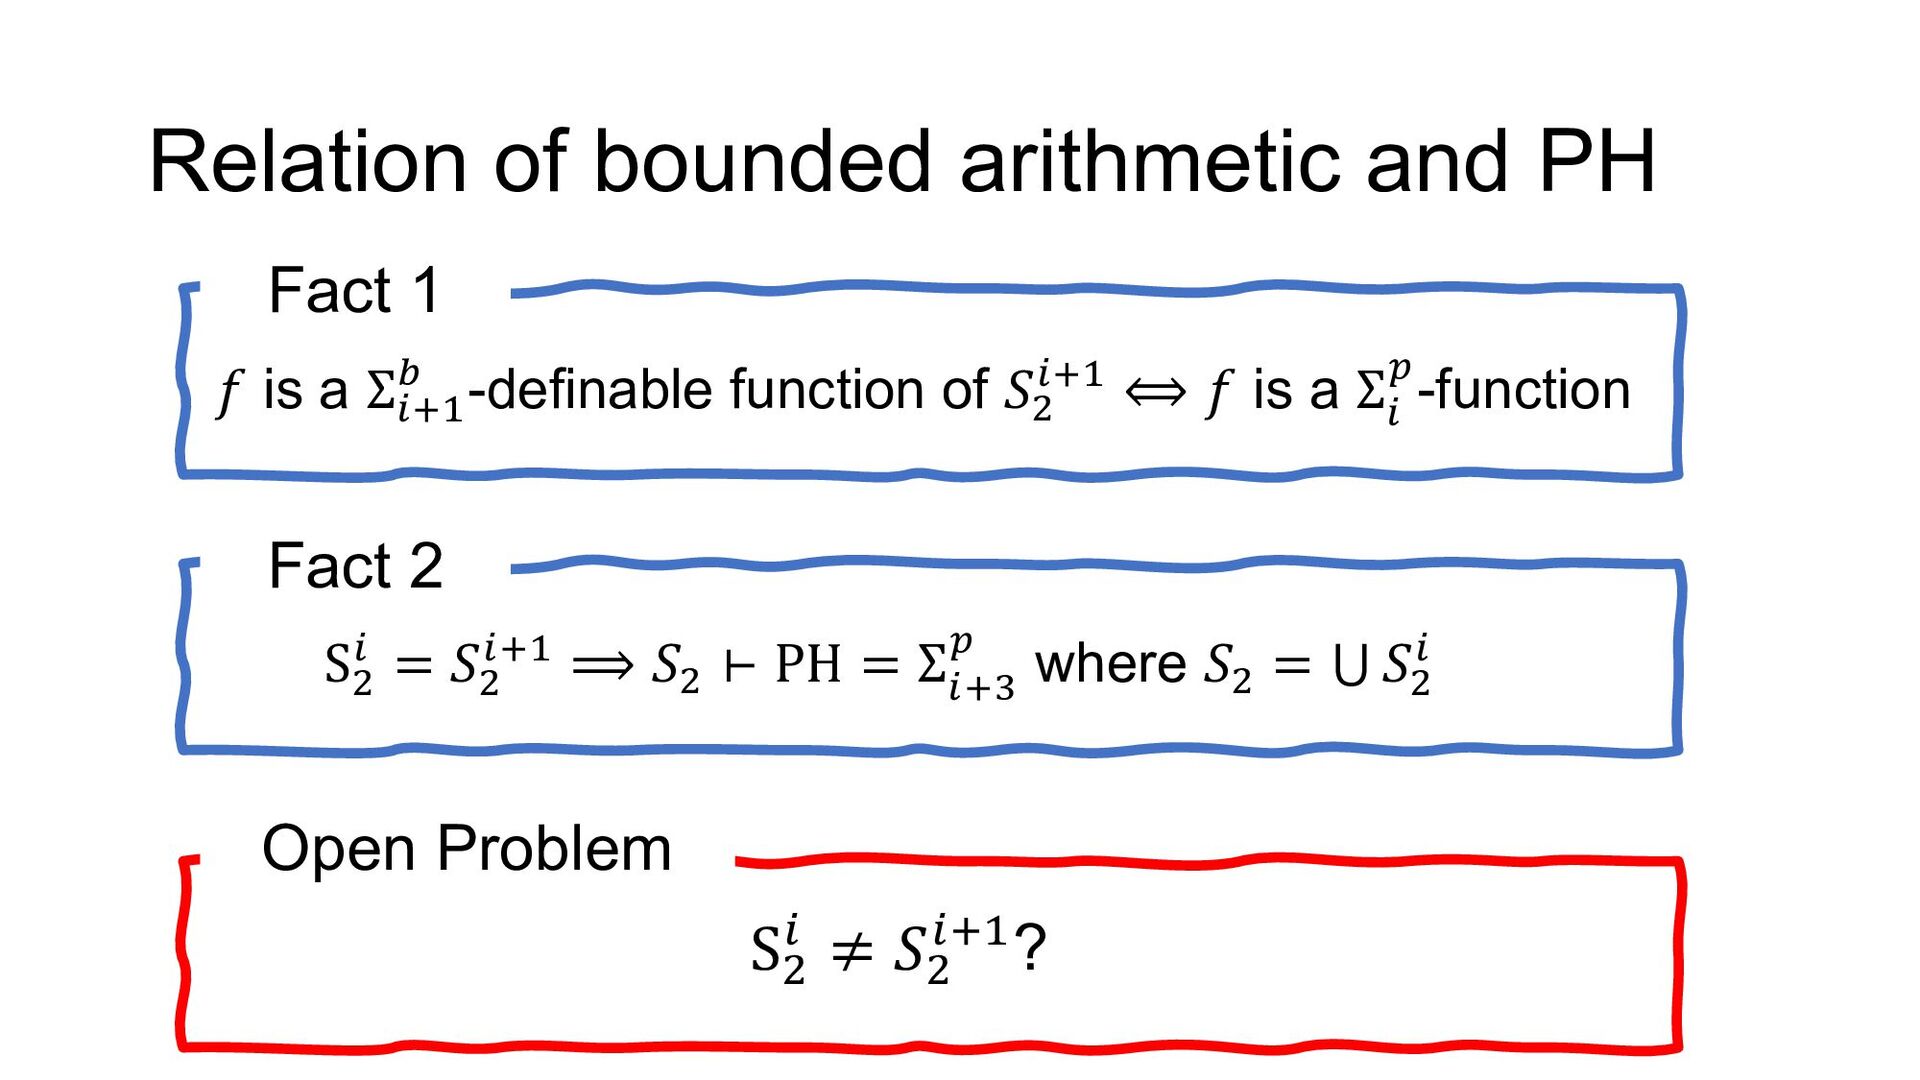
  7. Relation of bounded arithmetic and PH Fact 1 𝑓 is

    a Σ23# 1 -definable function of 𝑆. 23# ⟺ 𝑓 is a Σ2 $-function Fact 2 S. 2 = 𝑆. 23# ⟹ 𝑆. ⊢ PH = Σ 234 $ where 𝑆. = ⋃ 𝑆. 2 Open Problem S" & ≠ 𝑆" &'#?
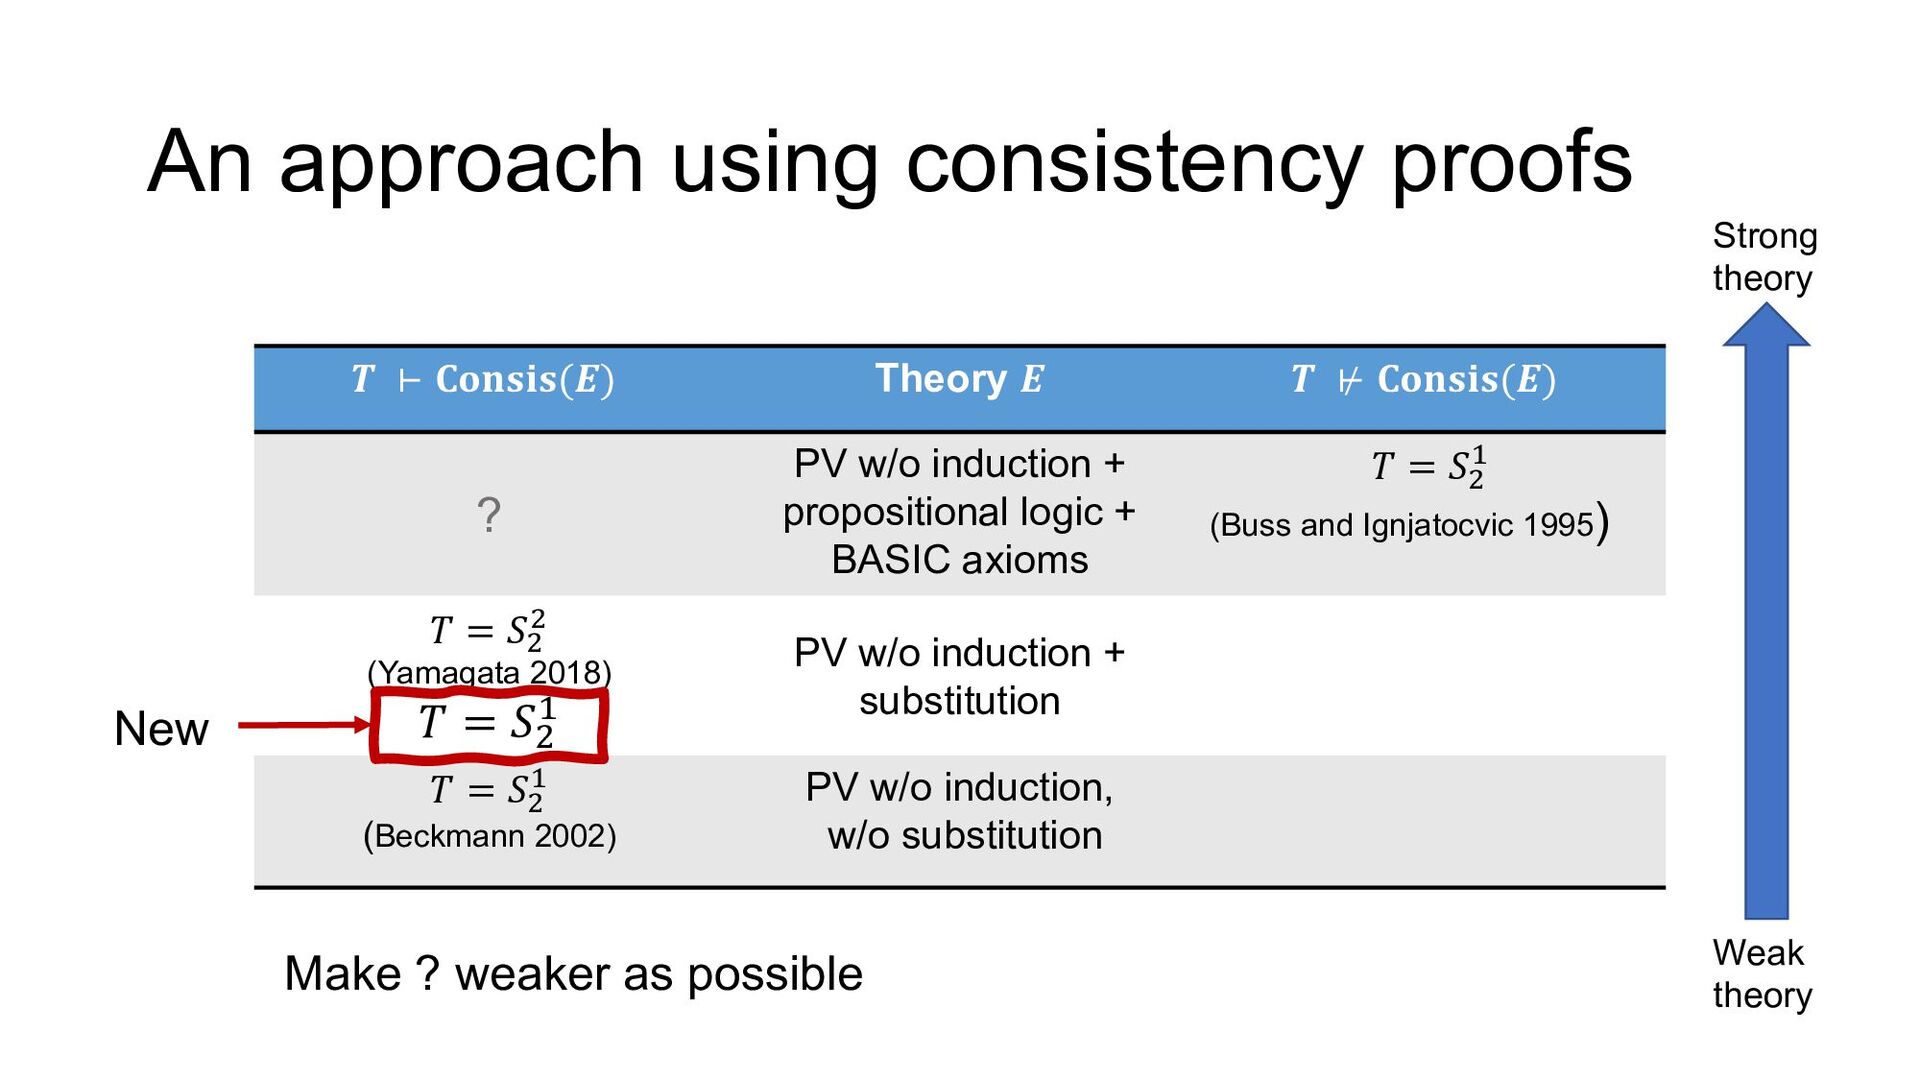
  8. 𝑻 ⊢ 𝐂𝐨𝐧𝐬𝐢𝐬(𝑬) Theory 𝑬 𝑻 ⊬ 𝐂𝐨𝐧𝐬𝐢𝐬(𝑬) ? PV

    w/o induction + propositional logic + BASIC axioms 𝑇 = 𝑆$ " (Buss and Ignjatocvic 1995) 𝑇 = 𝑆$ $ (Yamagata 2018) 𝑇 = 𝑆& % PV w/o induction + substitution 𝑇 = 𝑆$ " (Beckmann 2002) PV w/o induction, w/o substitution An approach using consistency proofs New Make ? weaker as possible Strong theory Weak theory
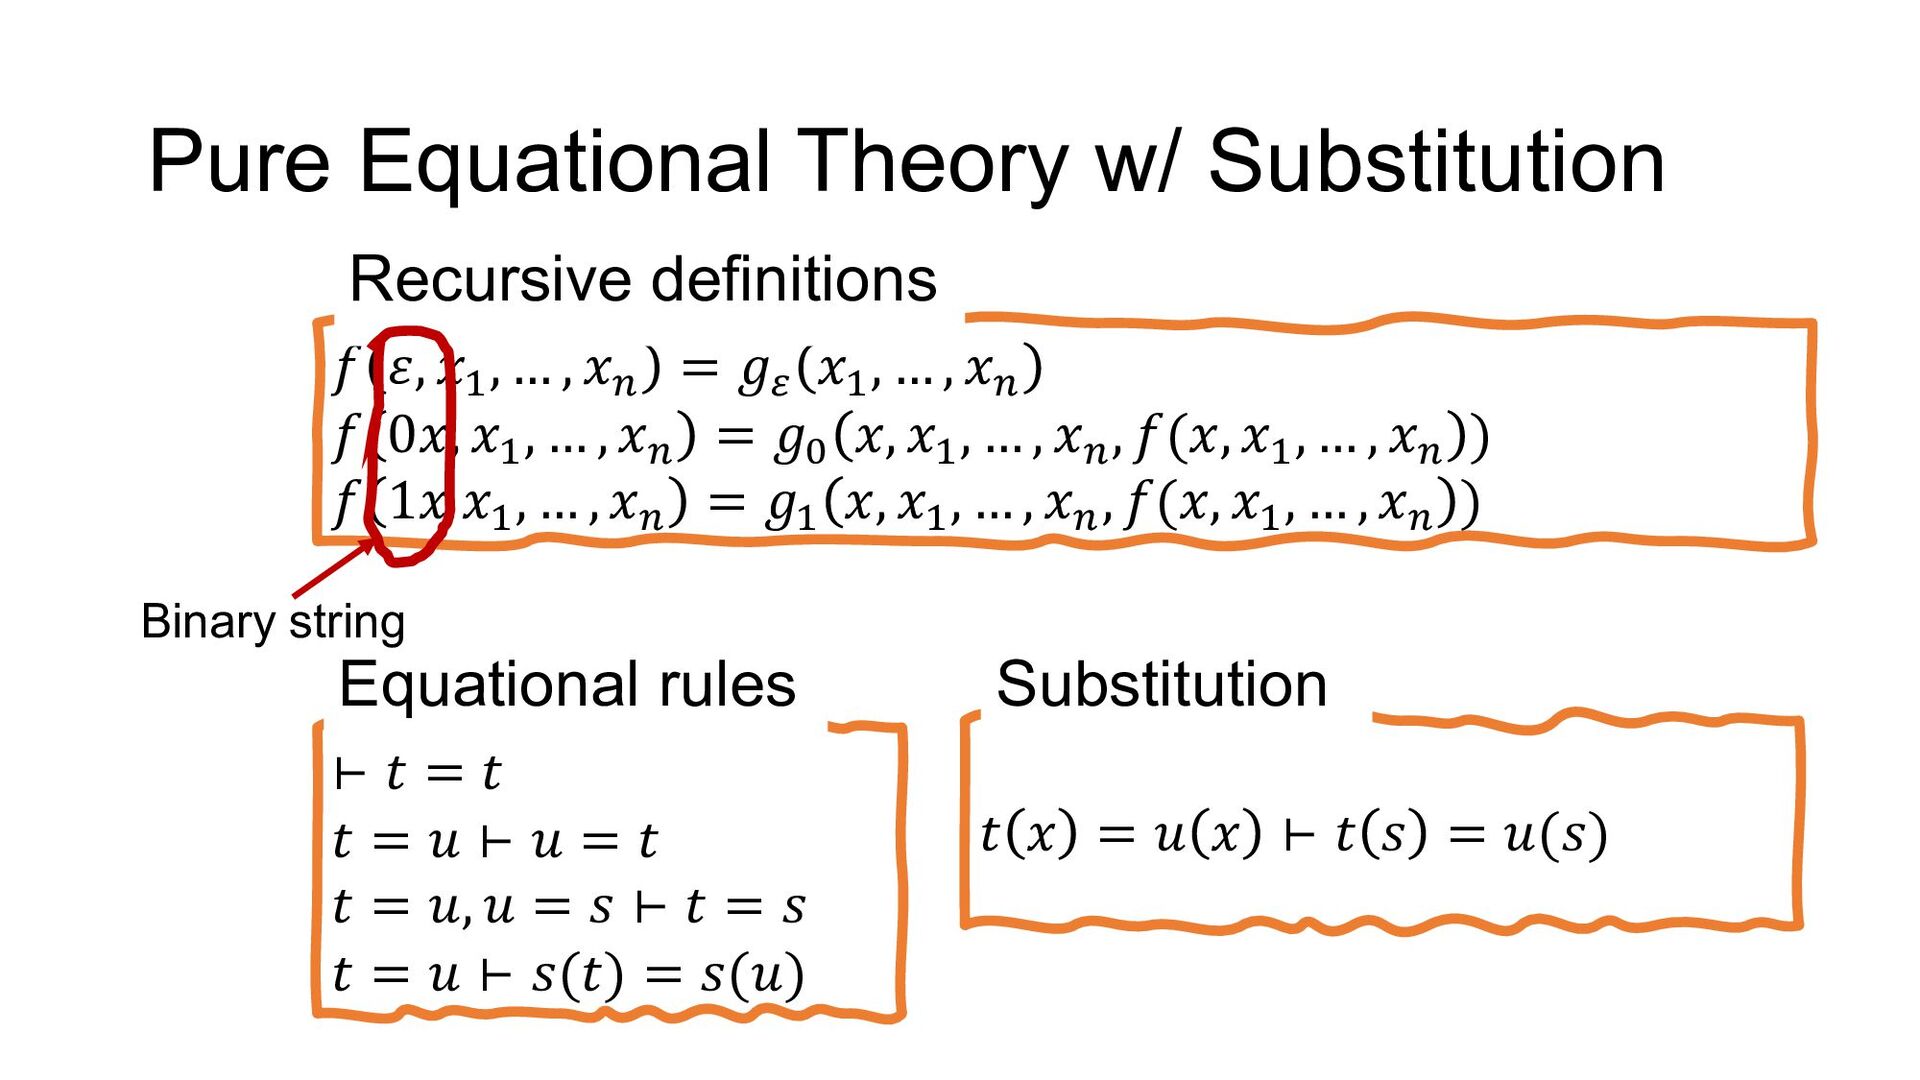
  9. Pure Equational Theory w/ Substitution 𝑓 𝜀, 𝑥# , …

    , 𝑥! = 𝑔A 𝑥# , … , 𝑥! 𝑓 0𝑥, 𝑥# , … , 𝑥! = 𝑔B 𝑥, 𝑥# , … , 𝑥! , 𝑓(𝑥, 𝑥# , … , 𝑥! ) 𝑓 1𝑥 𝑥# , … , 𝑥! = 𝑔# 𝑥, 𝑥# , … , 𝑥! , 𝑓(𝑥, 𝑥# , … , 𝑥! ) Recursive definitions ⊢ 𝑡 = 𝑡 𝑡 = 𝑢 ⊢ 𝑢 = 𝑡 𝑡 = 𝑢, 𝑢 = 𝑠 ⊢ 𝑡 = 𝑠 𝑡 = 𝑢 ⊢ 𝑠(𝑡) = 𝑠(𝑢) Equational rules 𝑡 𝑥 = 𝑢 𝑥 ⊢ 𝑡 𝑠 = 𝑢(𝑠) Substitution Binary string
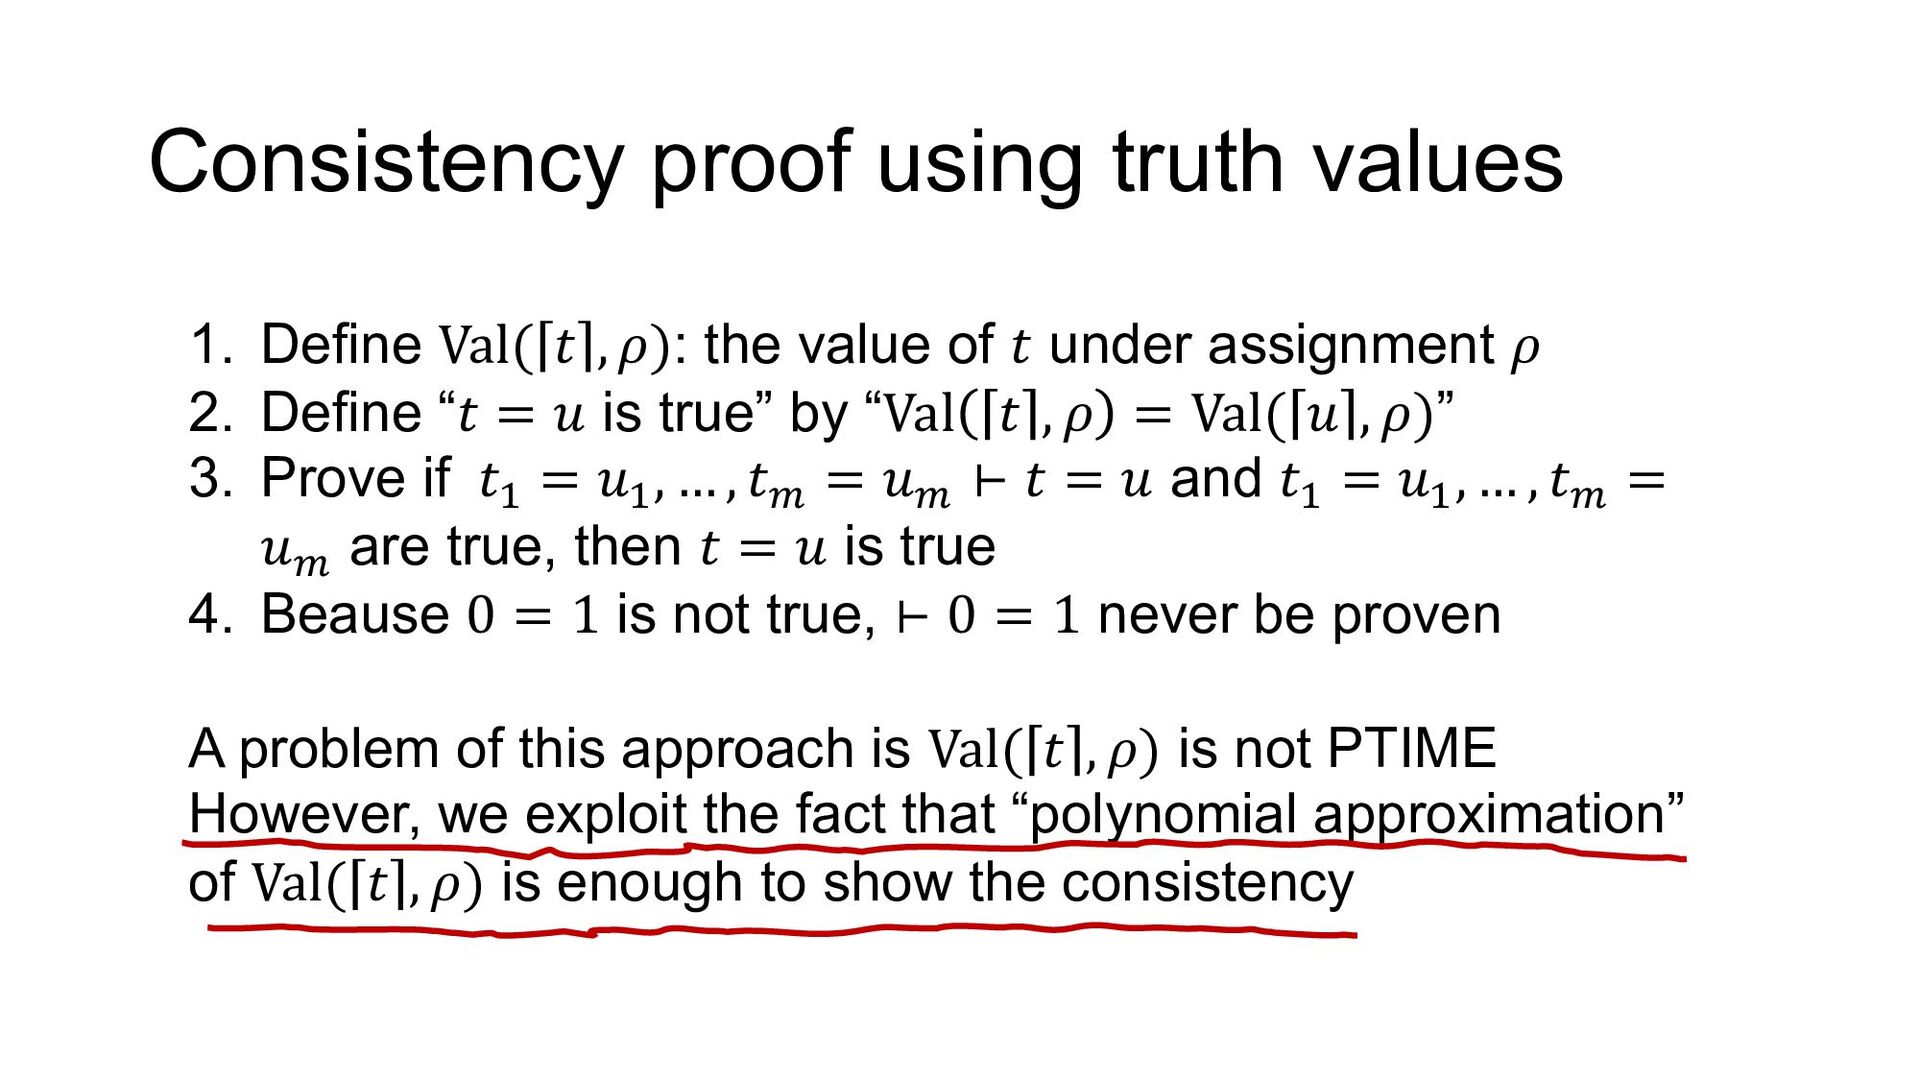
  10. Consistency proof using truth values 1. Define Val( 𝑡 ,

    𝜌): the value of 𝑡 under assignment 𝜌 2. Define “𝑡 = 𝑢 is true” by “Val 𝑡 , 𝜌 = Val( 𝑢 , 𝜌)” 3. Prove if 𝑡# = 𝑢# , … , 𝑡C = 𝑢C ⊢ 𝑡 = 𝑢 and 𝑡# = 𝑢# , … , 𝑡C = 𝑢C are true, then 𝑡 = 𝑢 is true 4. Beause 0 = 1 is not true, ⊢ 0 = 1 never be proven A problem of this approach is Val( 𝑡 , 𝜌) is not PTIME However, we exploit the fact that “polynomial approximation” of Val( 𝑡 , 𝜌) is enough to show the consistency
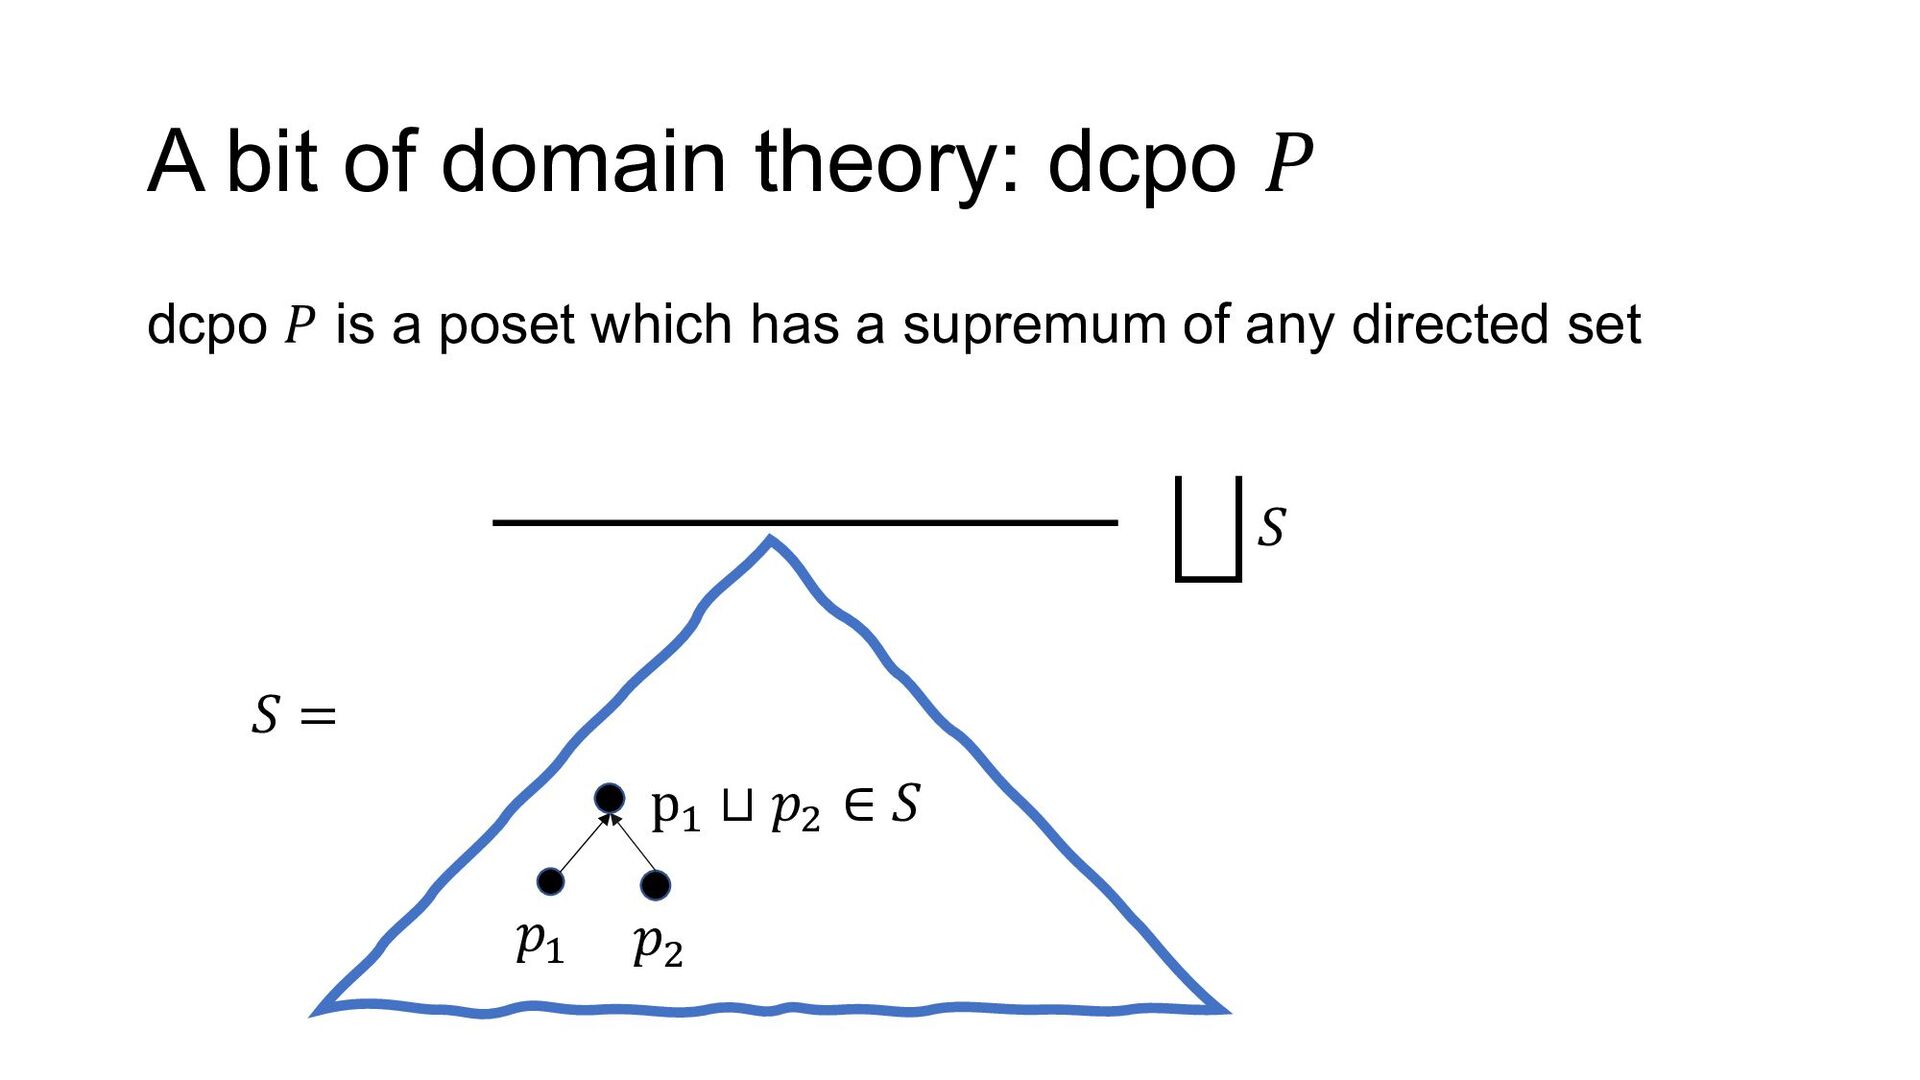
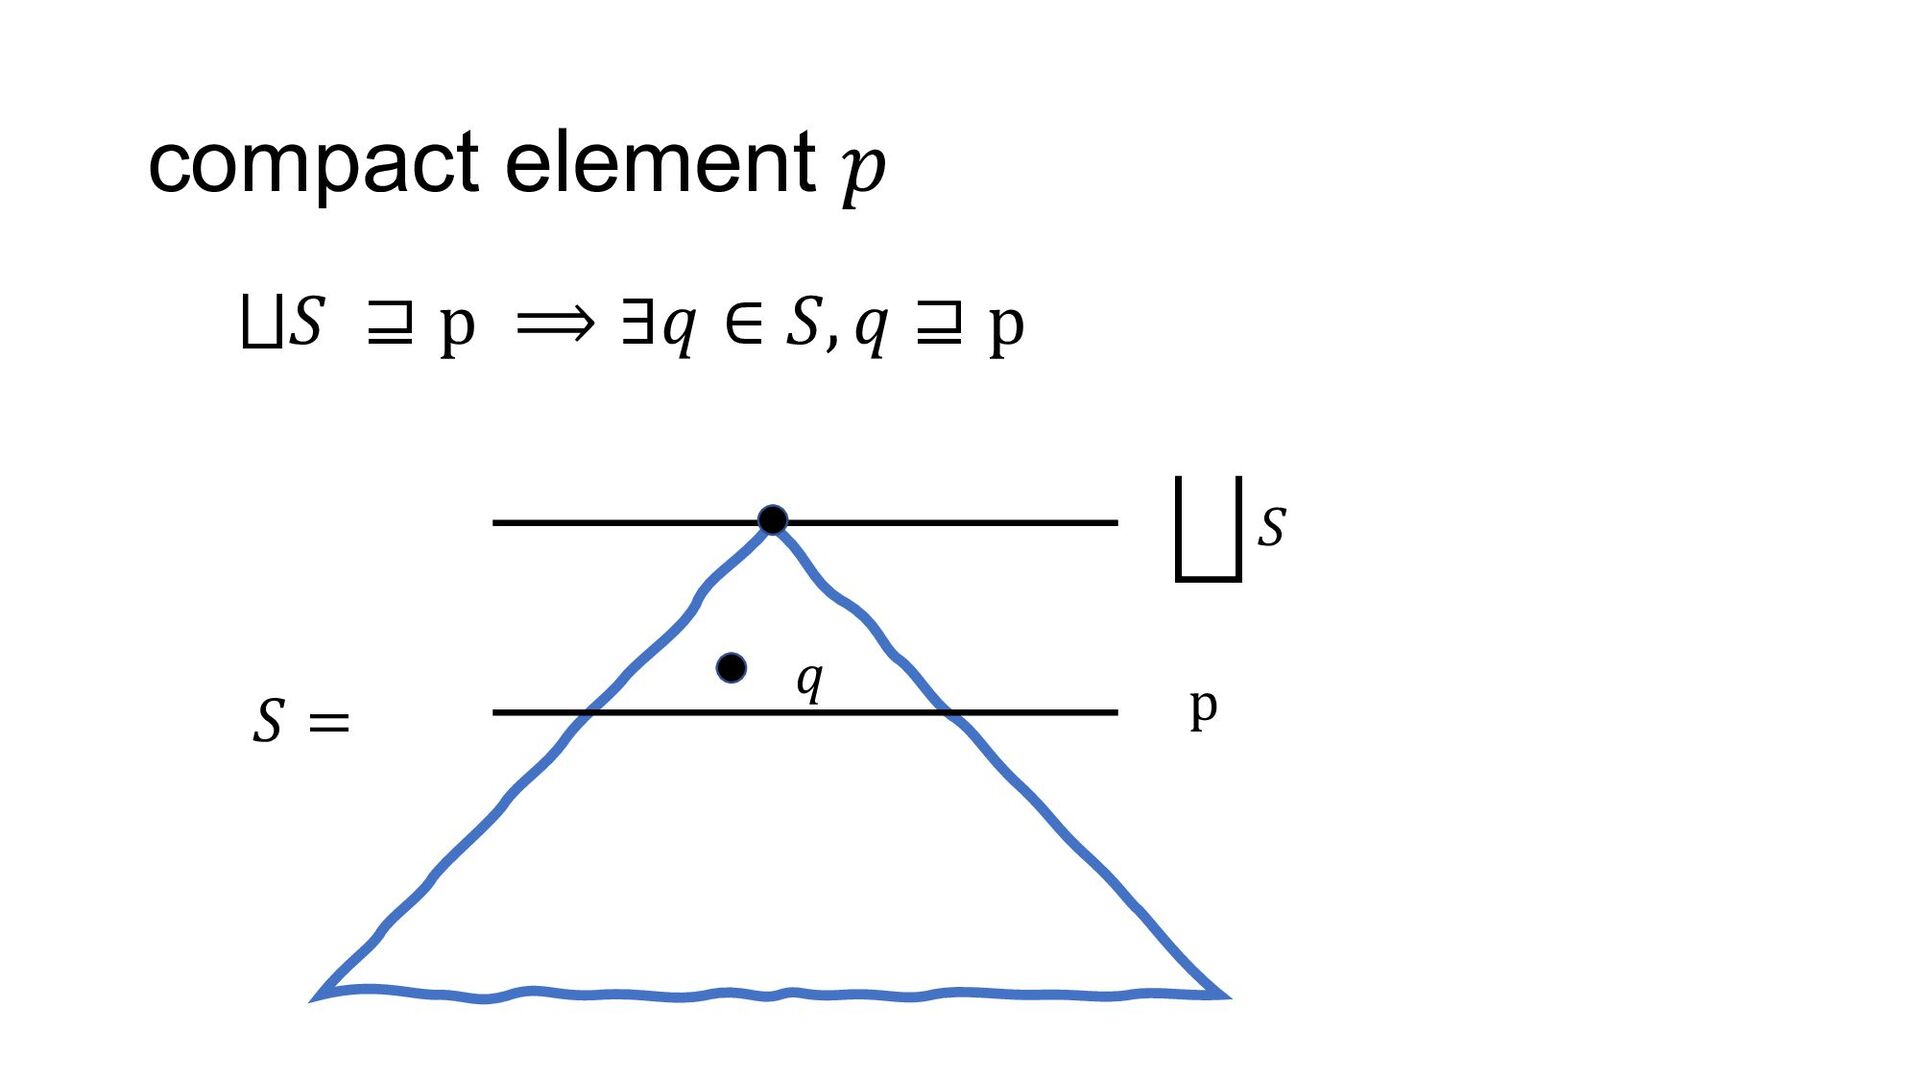
  11. A bit of domain theory: dcpo 𝑃 dcpo 𝑃 is

    a poset which has a supremum of any directed set 𝑝# 𝑝. 𝑆 = p# ⊔ 𝑝. ∈ 𝑆 H 𝑆
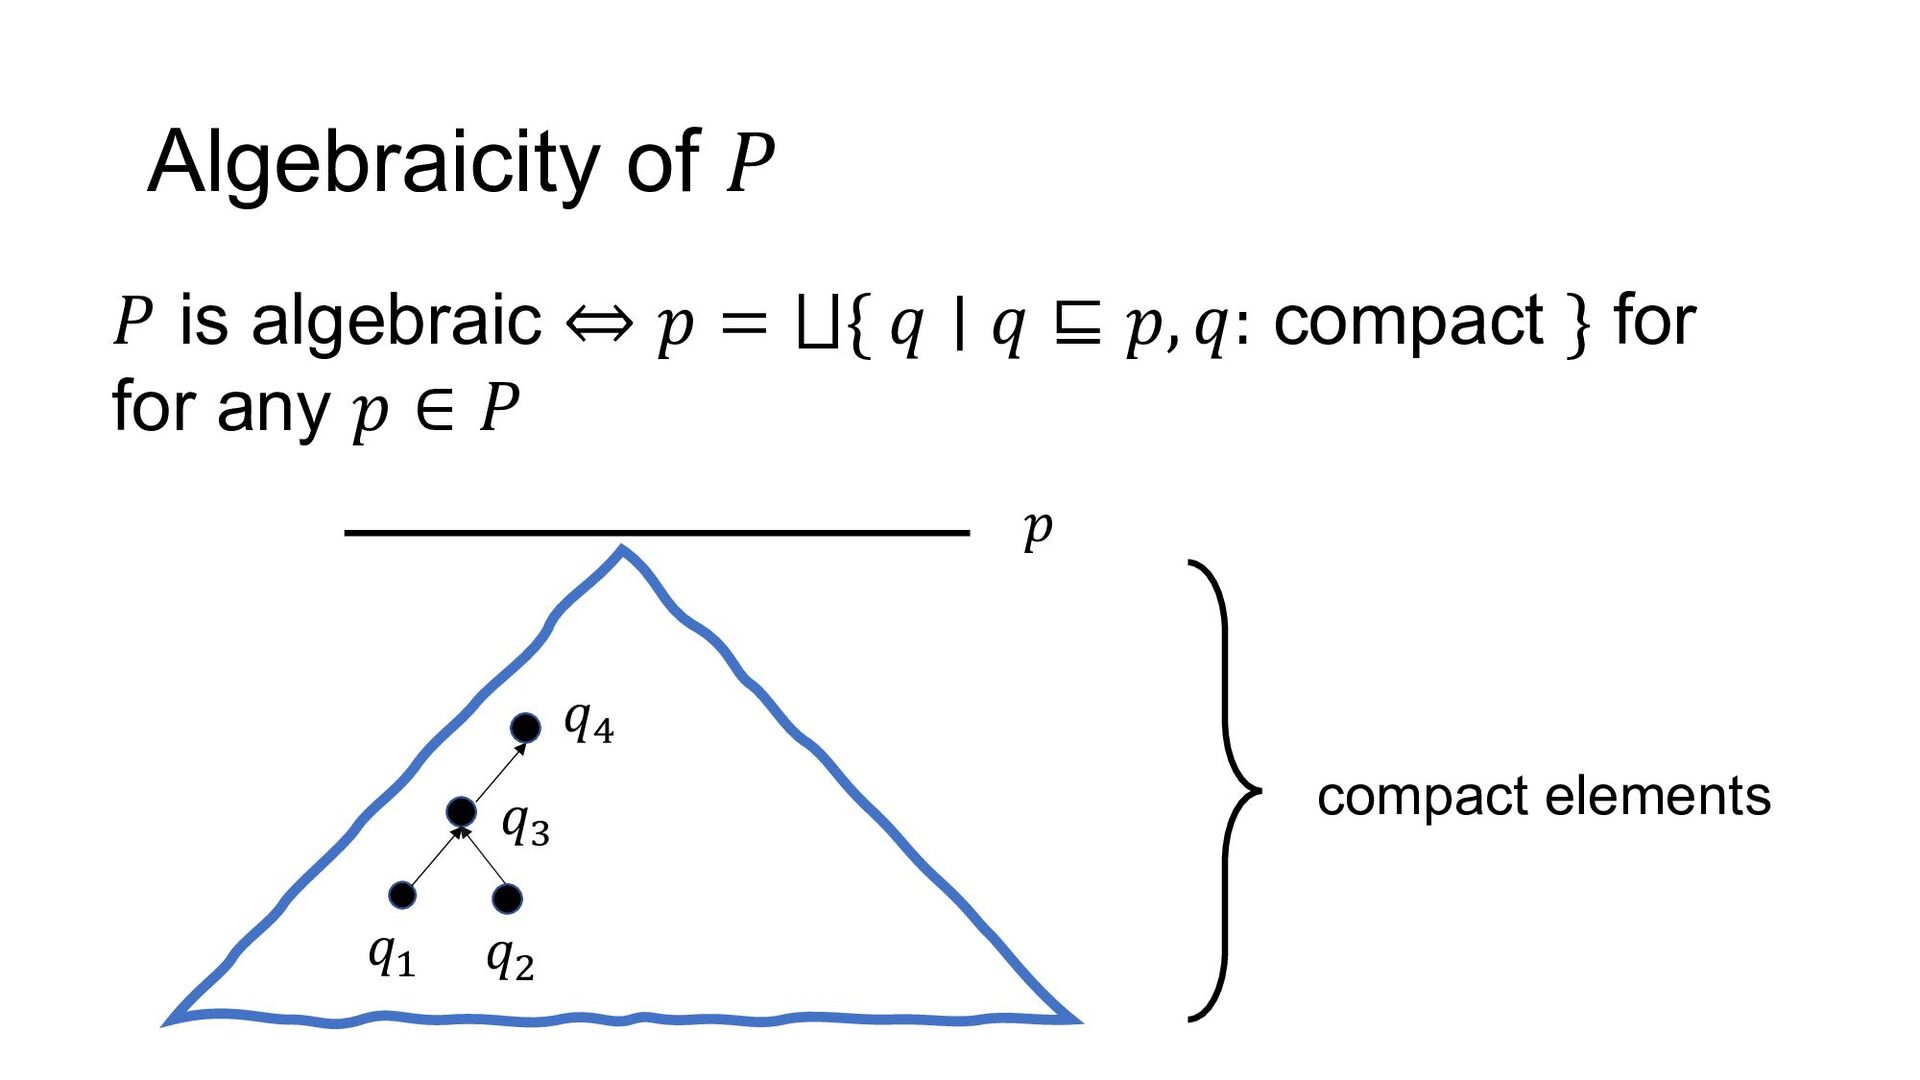
  12. Algebraicity of 𝑃 𝑃 is algebraic ⇔ 𝑝 = ⨆{

    𝑞 ∣ 𝑞 ⊑ 𝑝, 𝑞: compact } for for any 𝑝 ∈ 𝑃 𝑝 𝑞# 𝑞. 𝑞4 𝑞D compact elements
  13. Scott domain Nonempty poset 𝑃 is called “Scott domain” if

    •𝑃 is a dcpo •𝑃 is bounded complete, i.e., all bounded subsets have a supremum • 𝑃 is algebraic
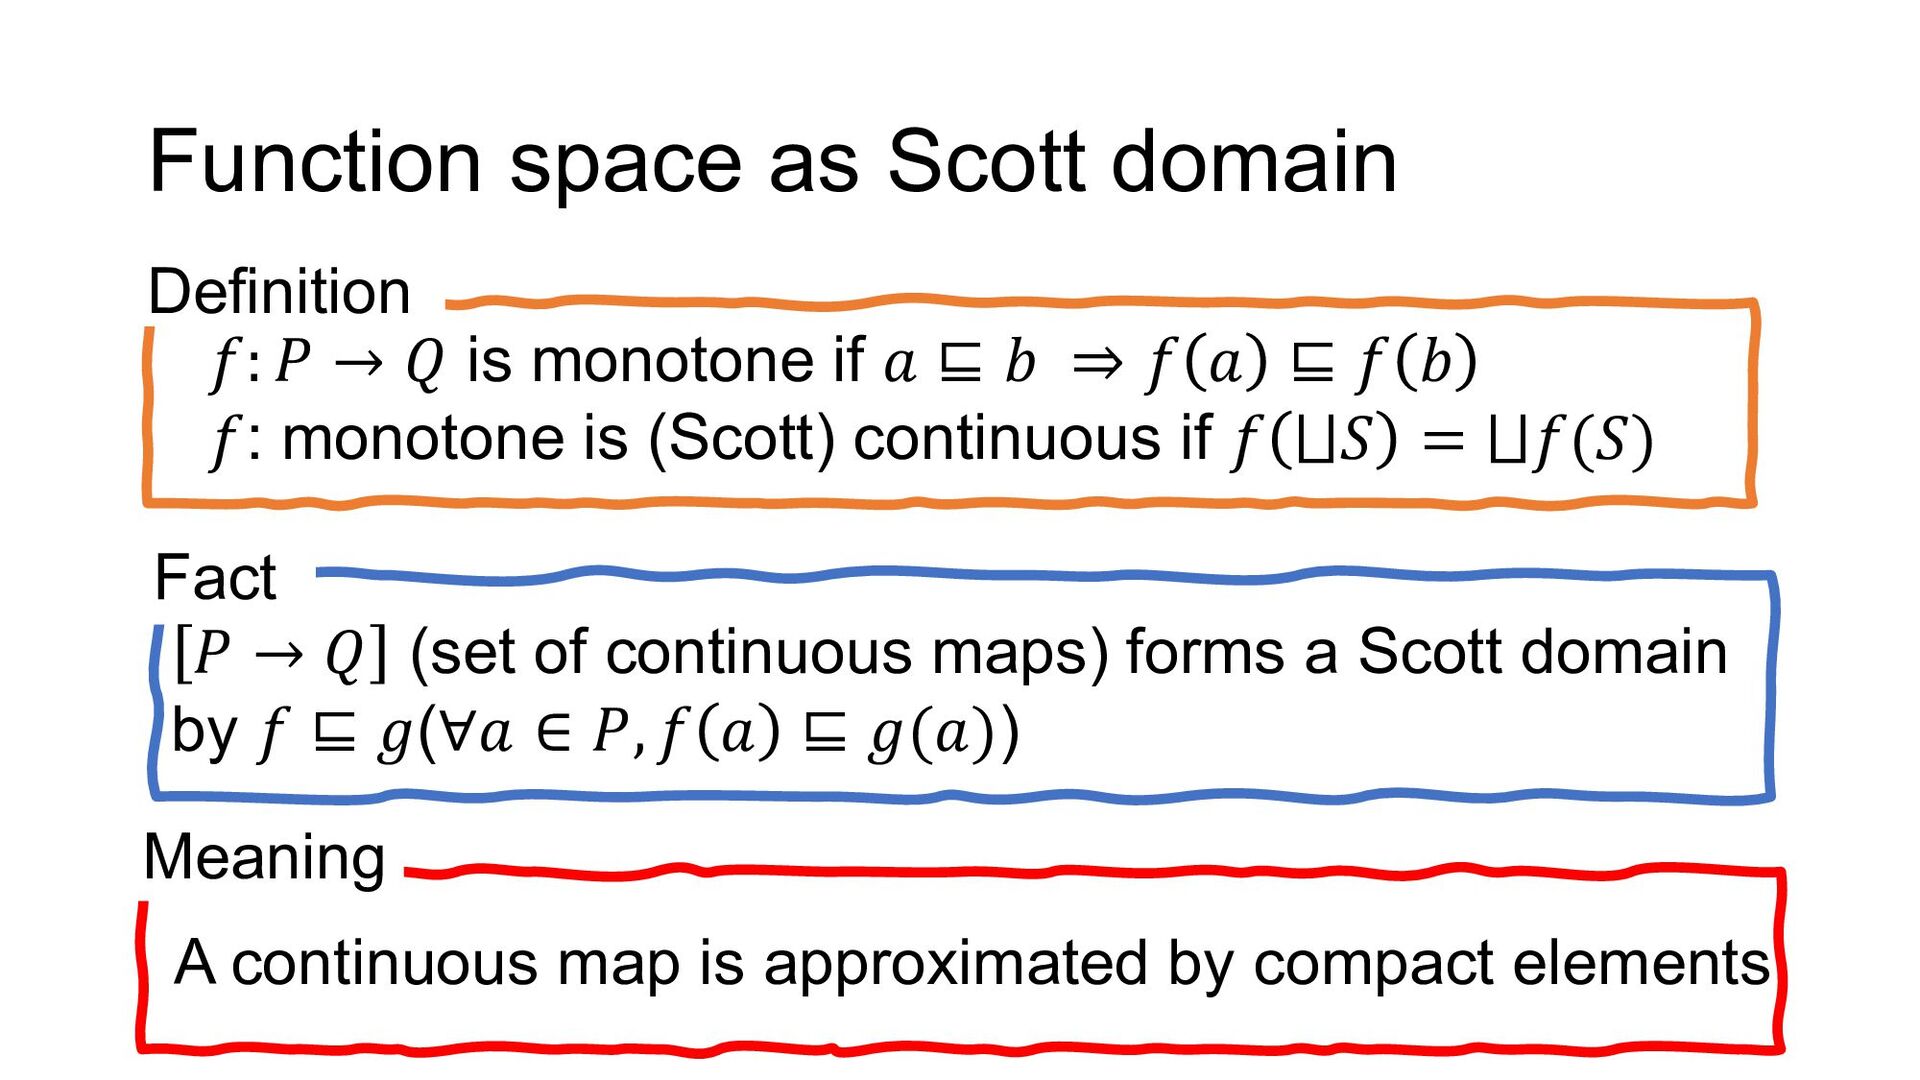
  14. Function space as Scott domain 𝑓: 𝑃 → 𝑄 is

    monotone if 𝑎 ⊑ 𝑏 ⇒ 𝑓 𝑎 ⊑ 𝑓 𝑏 𝑓: monotone is (Scott) continuous if 𝑓 ⨆𝑆 = ⨆𝑓(𝑆) Definition Fact 𝑃 → 𝑄 (set of continuous maps) forms a Scott domain by 𝑓 ⊑ 𝑔(∀𝑎 ∈ 𝑃, 𝑓 𝑎 ⊑ 𝑔(𝑎)) A continuous map is approximated by compact elements Meaning
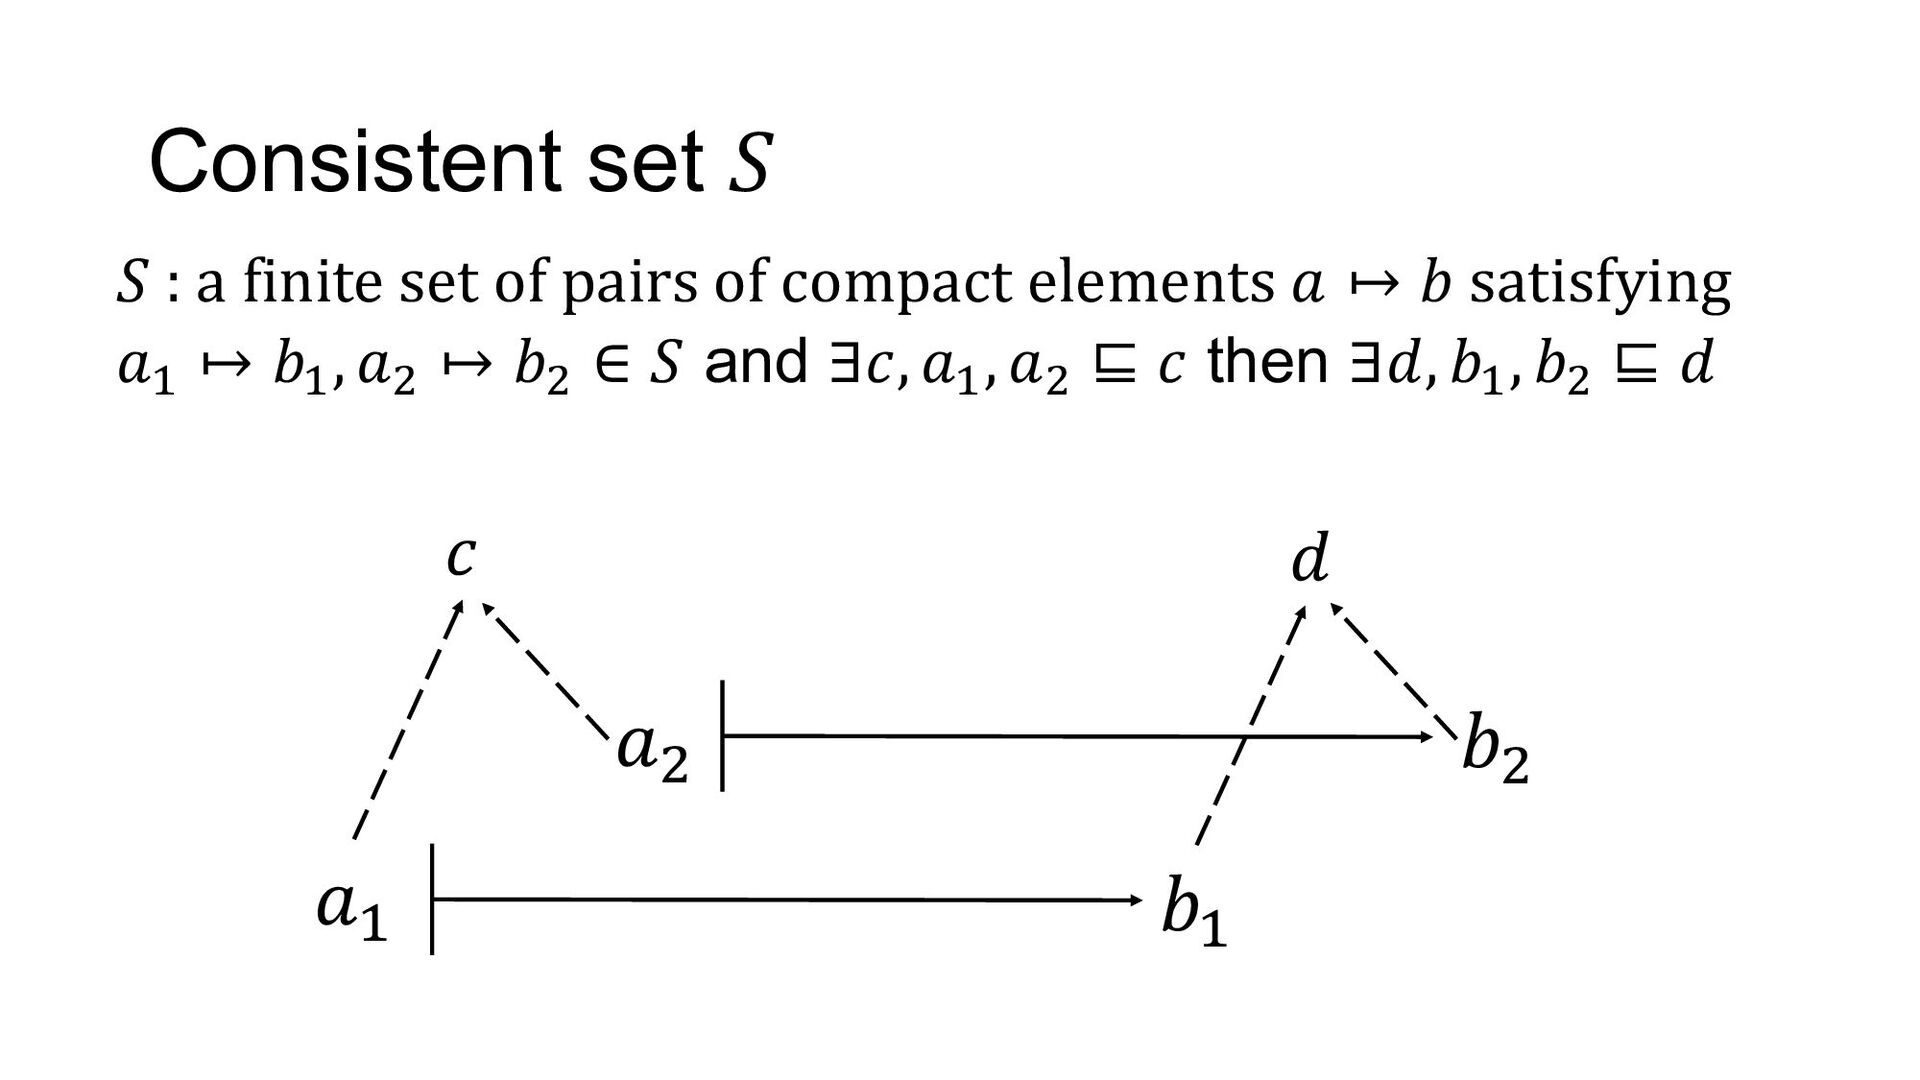
  15. Consistent set 𝑆 𝑆 : a finite set of pairs

    of compact elements 𝑎 ↦ 𝑏 satisfying 𝑎# ↦ 𝑏# , 𝑎" ↦ 𝑏" ∈ 𝑆 and ∃𝑐, 𝑎# , 𝑎" ⊑ 𝑐 then ∃𝑑, 𝑏# , 𝑏" ⊑ 𝑑 𝑎! 𝑎" 𝑐 𝑏! 𝑏" 𝑑
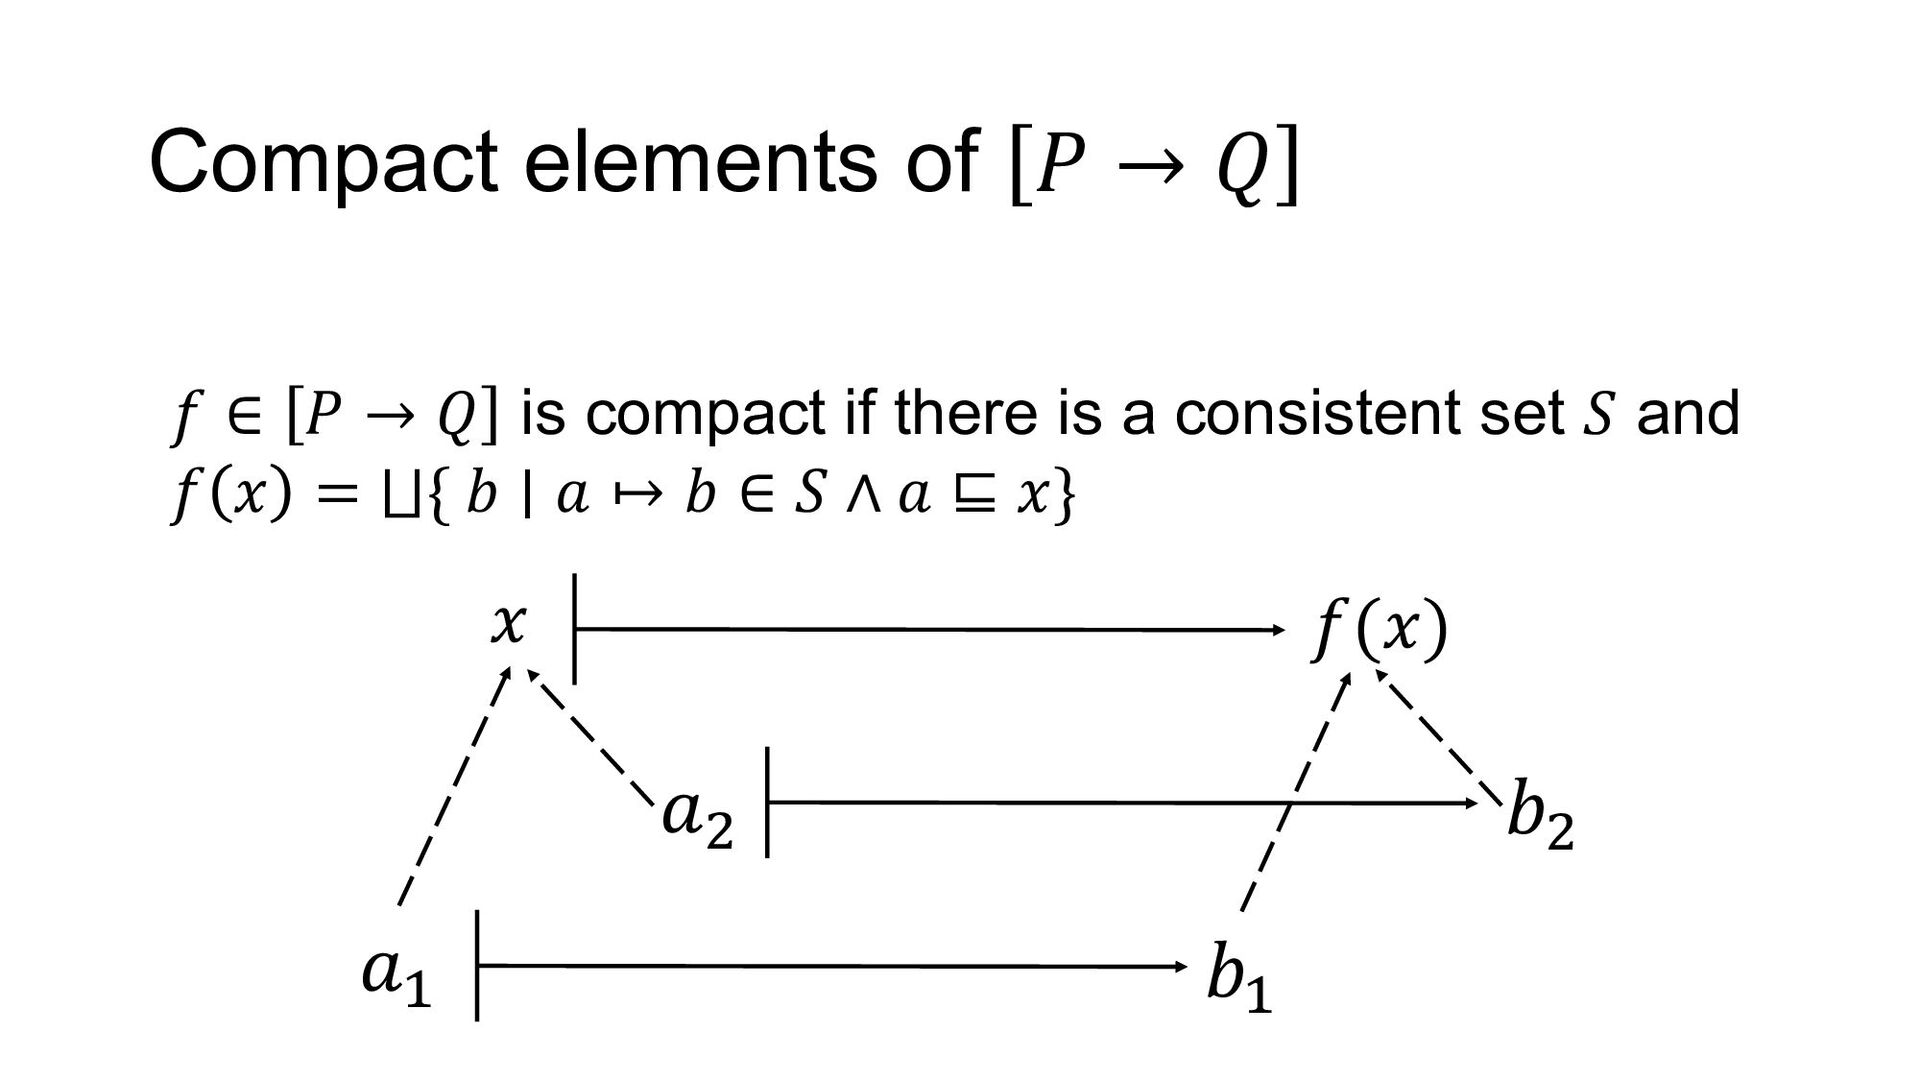
  16. Compact elements of 𝑃 → 𝑄 𝑓 ∈ 𝑃 →

    𝑄 is compact if there is a consistent set 𝑆 and 𝑓 𝑥 = ⨆{ 𝑏 ∣ 𝑎 ↦ 𝑏 ∈ 𝑆 ∧ 𝑎 ⊑ 𝑥} 𝑎! 𝑎" 𝑥 𝑏! 𝑏" 𝑓(𝑥)
  17. Our strategy to prove 𝑆2 ` ⊢ PETS • Define

    a domain • Show compacts elements approximating standard functions are enough to interpret a given deduction in PETS • Represents compacts elements by consistent sets • Show all operations on consistent sets are PTIME 𝐥(𝑠): number of symbols in an object 𝑠 (formula etc.) Definition
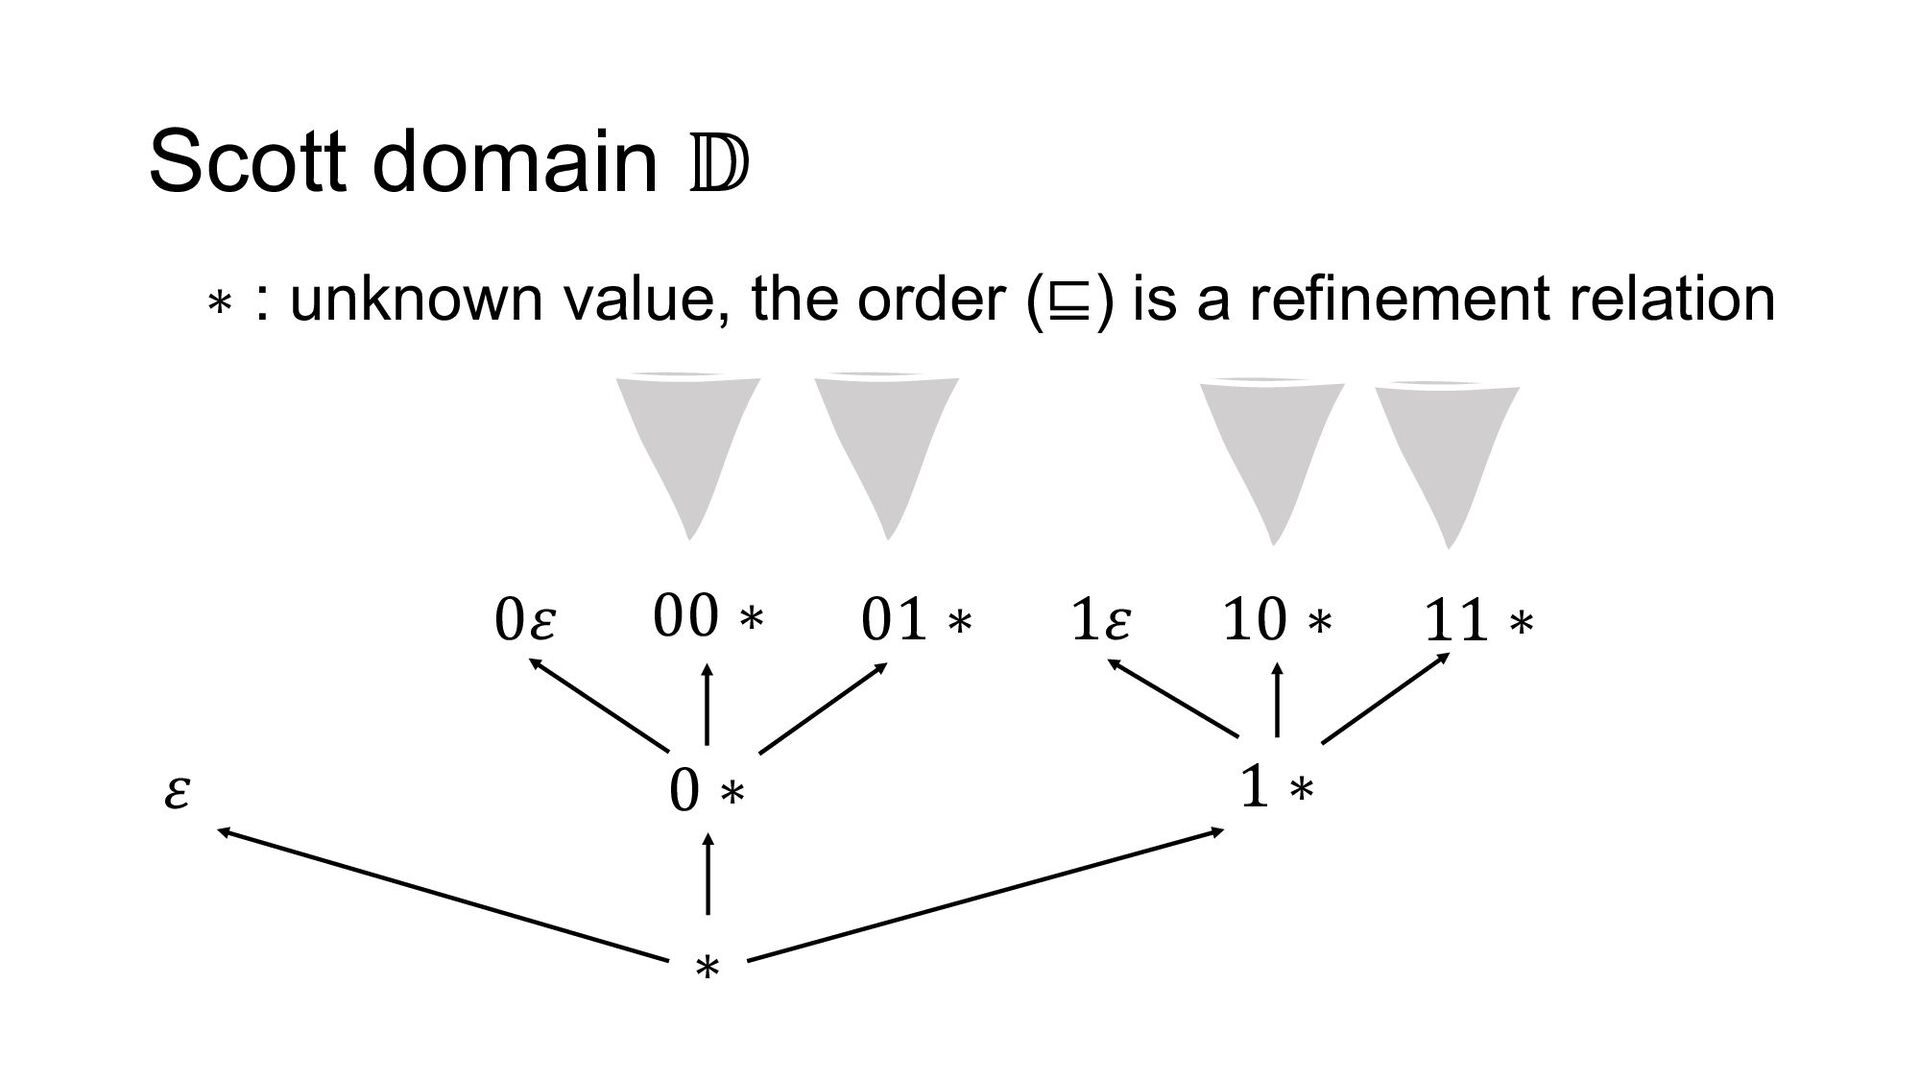
  18. Scott domain 𝔻 ∗ 𝜀 0 ∗ 1 ∗ 0𝜀

    00 ∗ 01 ∗ 1𝜀 10 ∗ 11 ∗ ∗ : unknown value, the order (⊑) is a refinement relation
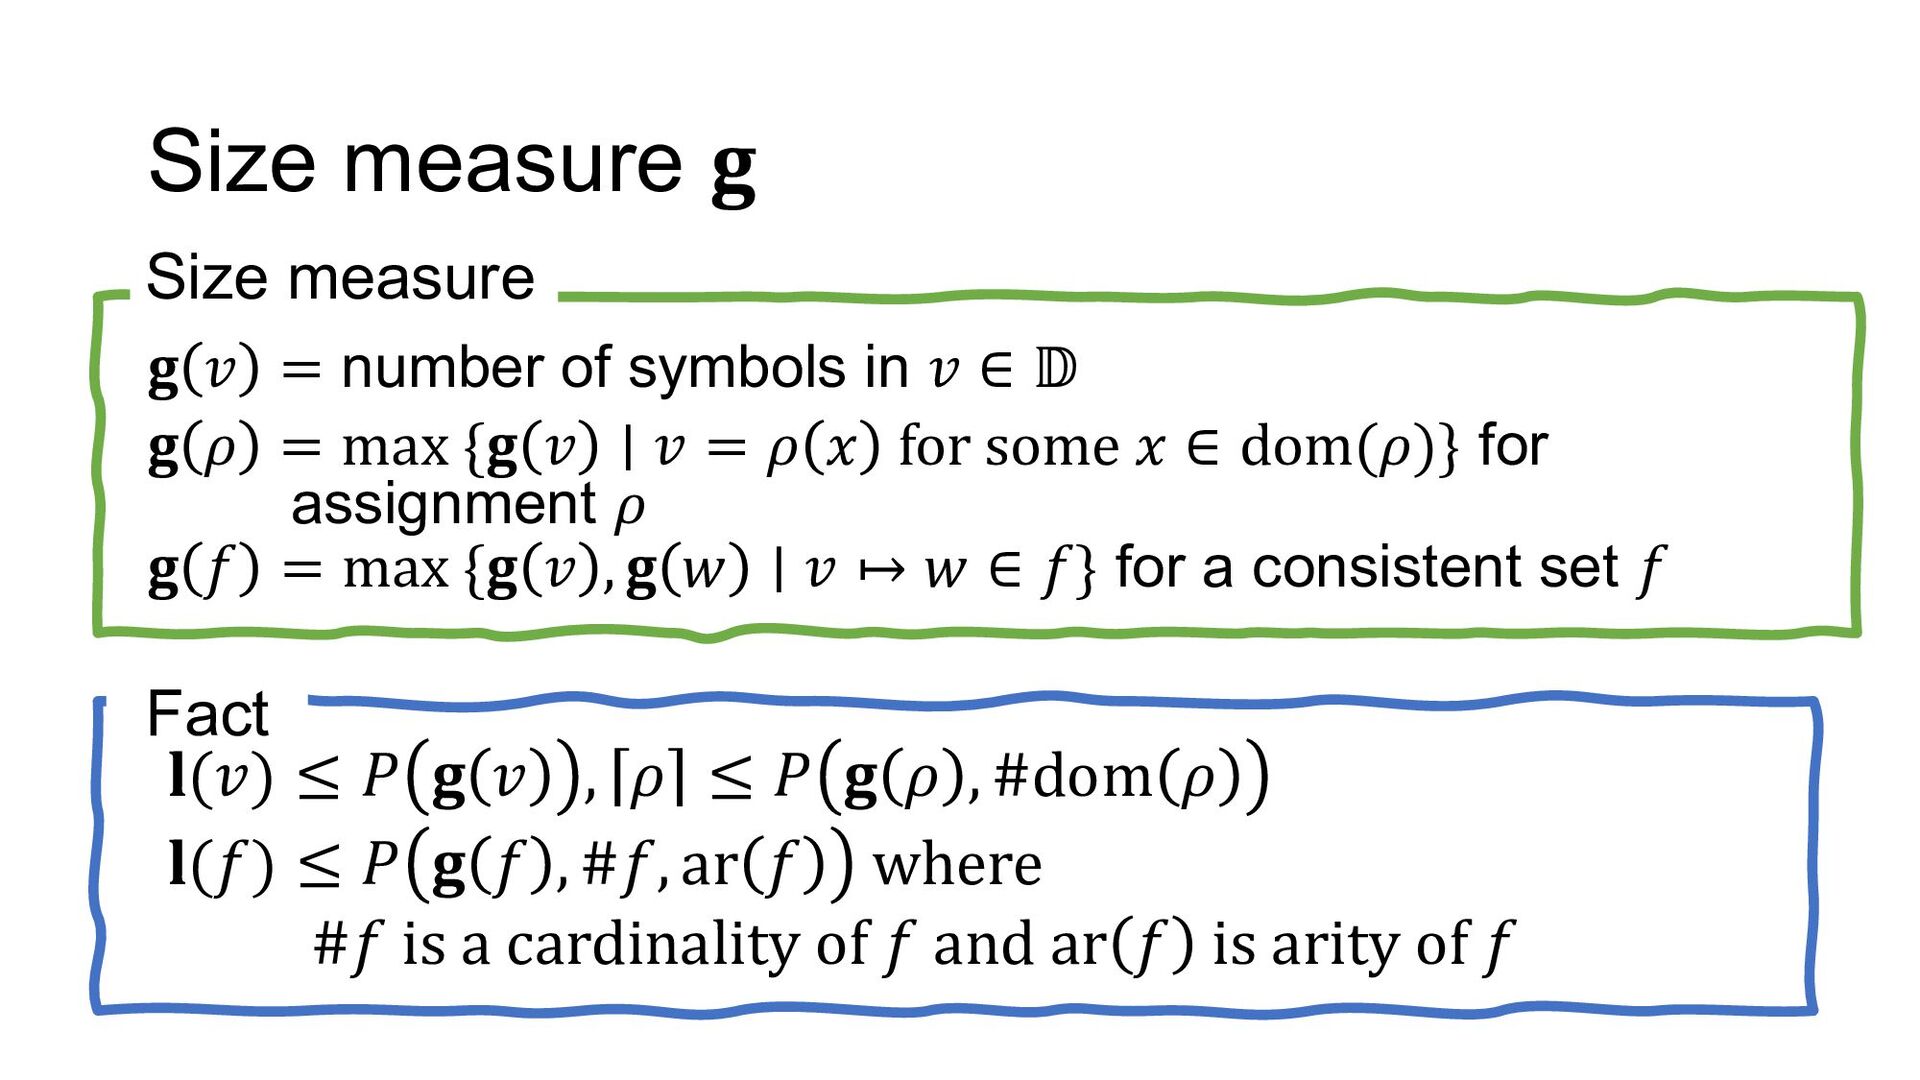
  19. Size measure Size measure 𝐠 𝐠 𝑣 = number of

    symbols in 𝑣 ∈ 𝔻 𝐠 𝜌 = max {𝐠 𝑣 ∣ 𝑣 = 𝜌 𝑥 for some 𝑥 ∈ dom(𝜌)} for assignment 𝜌 𝐠 𝑓 = max {𝐠 𝑣 , 𝐠 𝑤 ∣ 𝑣 ↦ 𝑤 ∈ 𝑓} for a consistent set 𝑓 Fact 𝐥(𝑣) ≤ 𝑃 𝐠 𝑣 , 𝜌 ≤ 𝑃 𝐠 𝜌 , #dom 𝜌 𝐥(𝑓) ≤ 𝑃 𝐠 𝑓 , #𝑓, ar 𝑓 where #𝑓 is a cardinality of 𝑓 and ar 𝑓 is arity of 𝑓
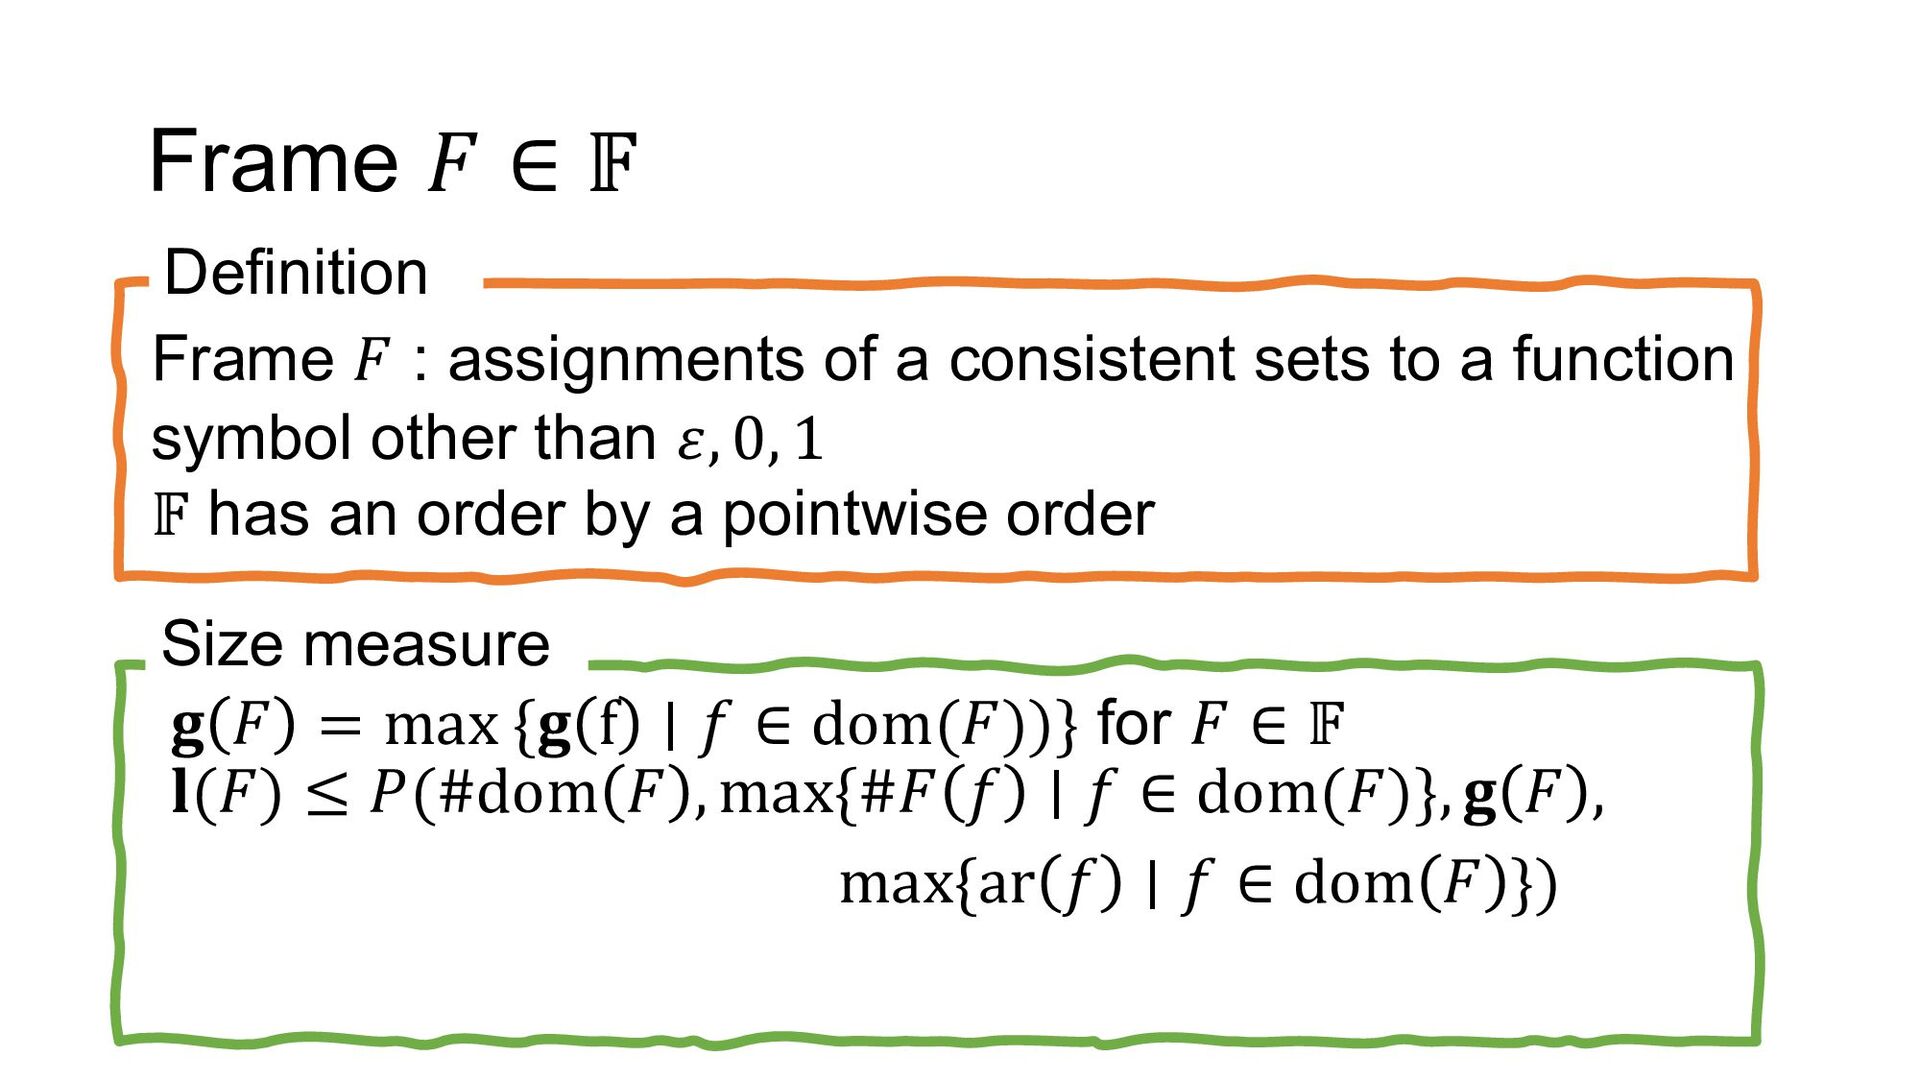
  20. Frame 𝐹 ∈ 𝔽 Frame 𝐹 : assignments of a

    consistent sets to a function symbol other than 𝜀, 0, 1 𝔽 has an order by a pointwise order Definition Size measure 𝐠 𝐹 = max {𝐠 f ∣ 𝑓 ∈ dom(𝐹))} for 𝐹 ∈ 𝔽 𝐥(𝐹) ≤ 𝑃(#dom 𝐹 , max{#𝐹 𝑓 ∣ 𝑓 ∈ dom(𝐹)}, 𝐠 𝐹 , max{ar 𝑓 ∣ 𝑓 ∈ dom 𝐹 })
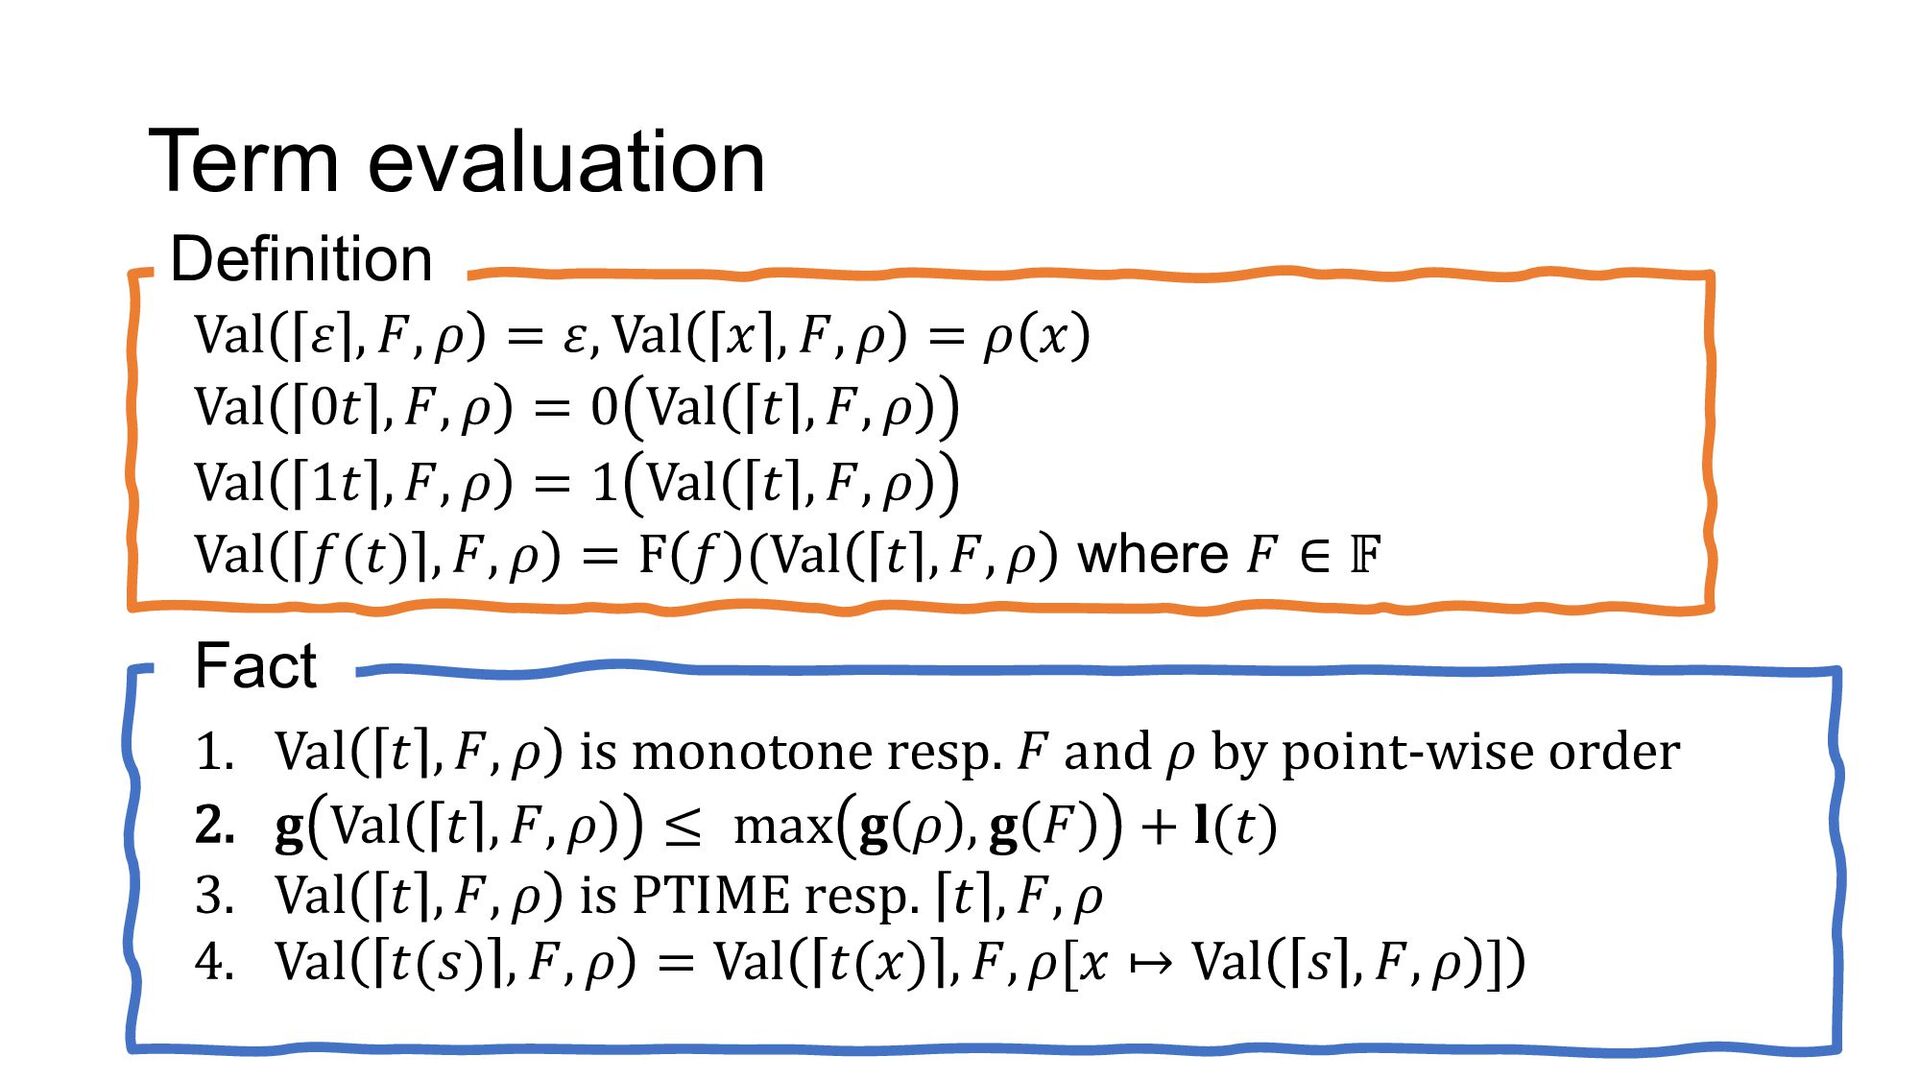
  21. Term evaluation Val 𝜀 , 𝐹, 𝜌 = 𝜀, Val

    𝑥 , 𝐹, 𝜌 = 𝜌 𝑥 Val 0𝑡 , 𝐹, 𝜌 = 0 Val 𝑡 , 𝐹, 𝜌 Val 1𝑡 , 𝐹, 𝜌 = 1 Val 𝑡 , 𝐹, 𝜌 Val 𝑓(𝑡) , 𝐹, 𝜌 = F 𝑓 (Val 𝑡 , 𝐹, 𝜌 where 𝐹 ∈ 𝔽 Definition Fact 1. Val 𝑡 , 𝐹, 𝜌 is monotone resp. 𝐹 and 𝜌 by point-wise order 2. 𝐠 Val 𝑡 , 𝐹, 𝜌 ≤ max 𝐠 𝜌 , 𝐠 𝐹 + 𝐥(𝑡) 3. Val 𝑡 , 𝐹, 𝜌 is PTIME resp. 𝑡 , 𝐹, 𝜌 4. Val 𝑡(𝑠) , 𝐹, 𝜌 = Val 𝑡(𝑥) , 𝐹, 𝜌[𝑥 ↦ Val 𝑠 , 𝐹, 𝜌 ]
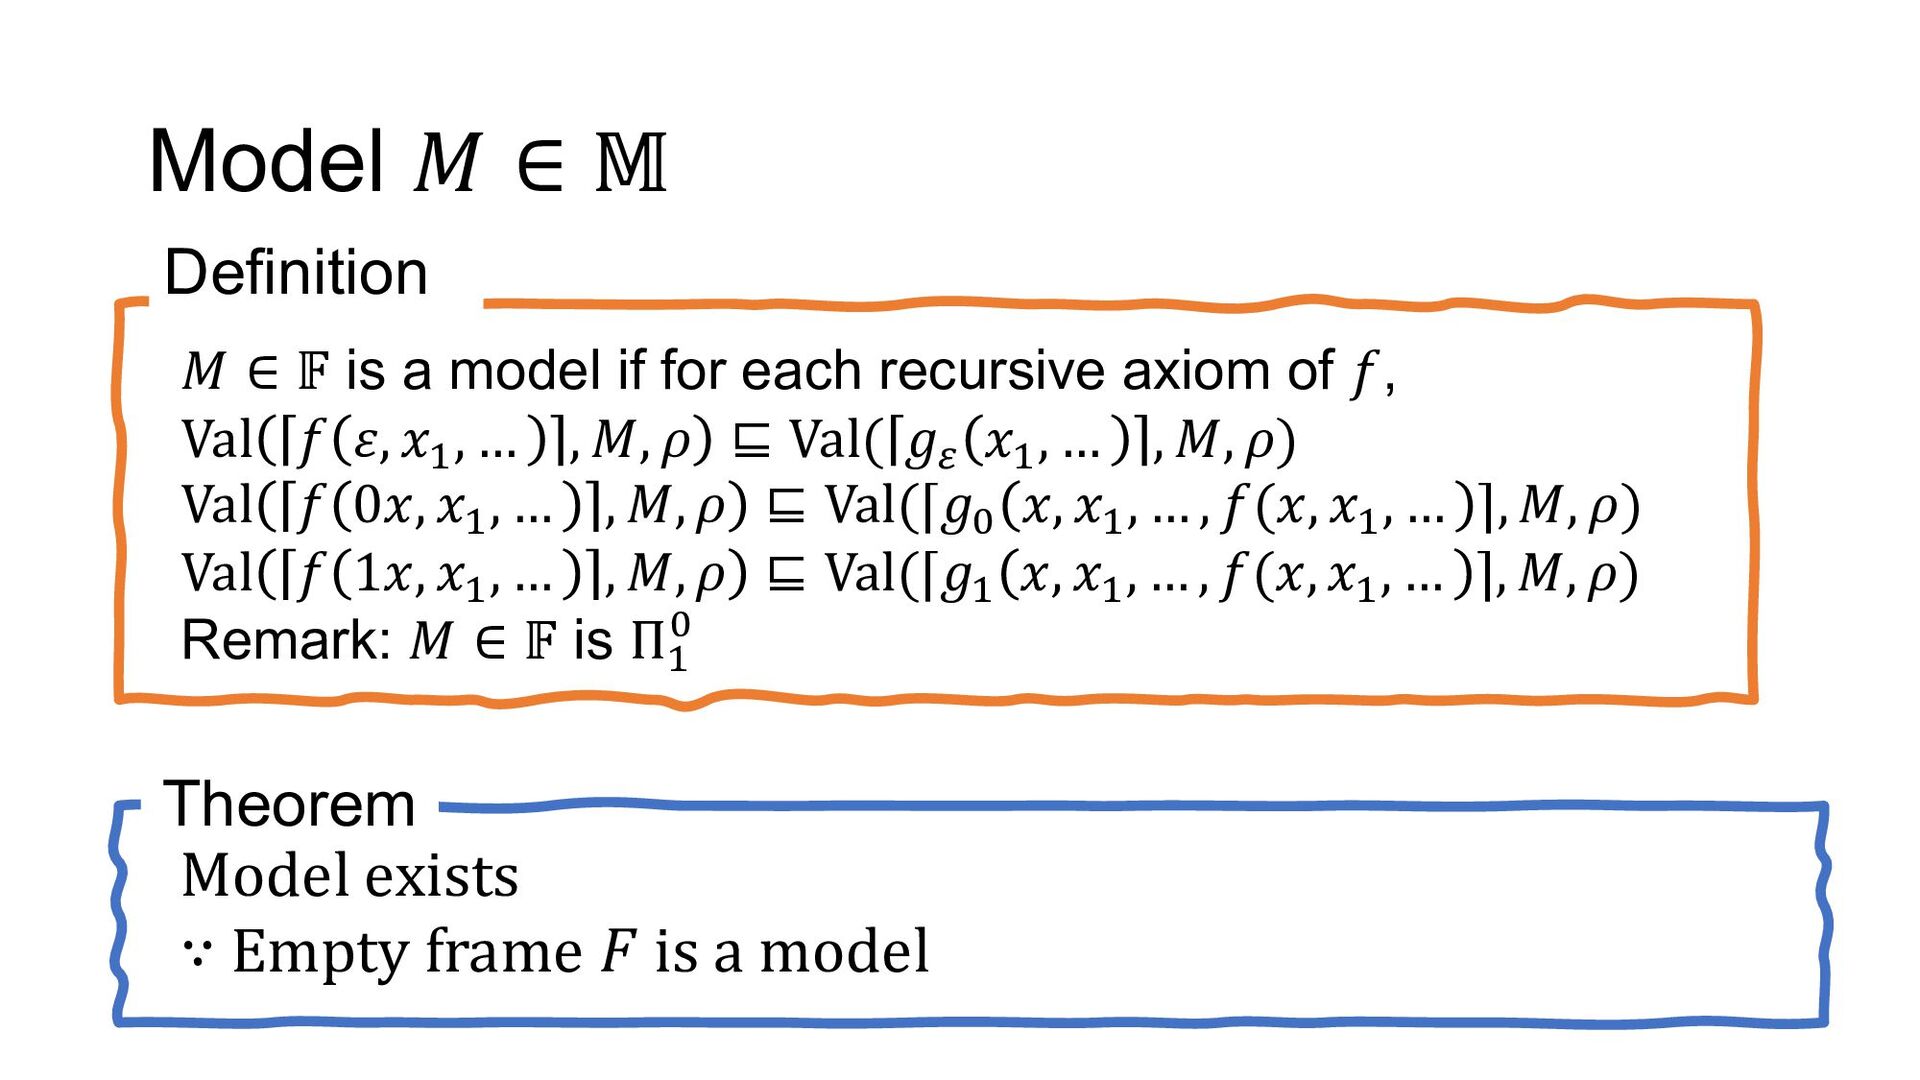
  22. Model 𝑀 ∈ 𝕄 𝑀 ∈ 𝔽 is a model

    if for each recursive axiom of 𝑓, Val 𝑓 𝜀, 𝑥# , … , 𝑀, 𝜌 ⊑ Val( 𝑔A 𝑥# , … , 𝑀, 𝜌) Val 𝑓 0𝑥, 𝑥# , … , 𝑀, 𝜌 ⊑ Val(⌈𝑔B 𝑥, 𝑥# , … , 𝑓(𝑥, 𝑥# , … ⌉, 𝑀, 𝜌) Val 𝑓 1𝑥, 𝑥# , … , 𝑀, 𝜌 ⊑ Val(⌈𝑔# 𝑥, 𝑥# , … , 𝑓(𝑥, 𝑥# , … ⌉, 𝑀, 𝜌) Remark: 𝑀 ∈ 𝔽 is Π# B Definition Theorem Model exists ∵ Empty frame 𝐹 is a model
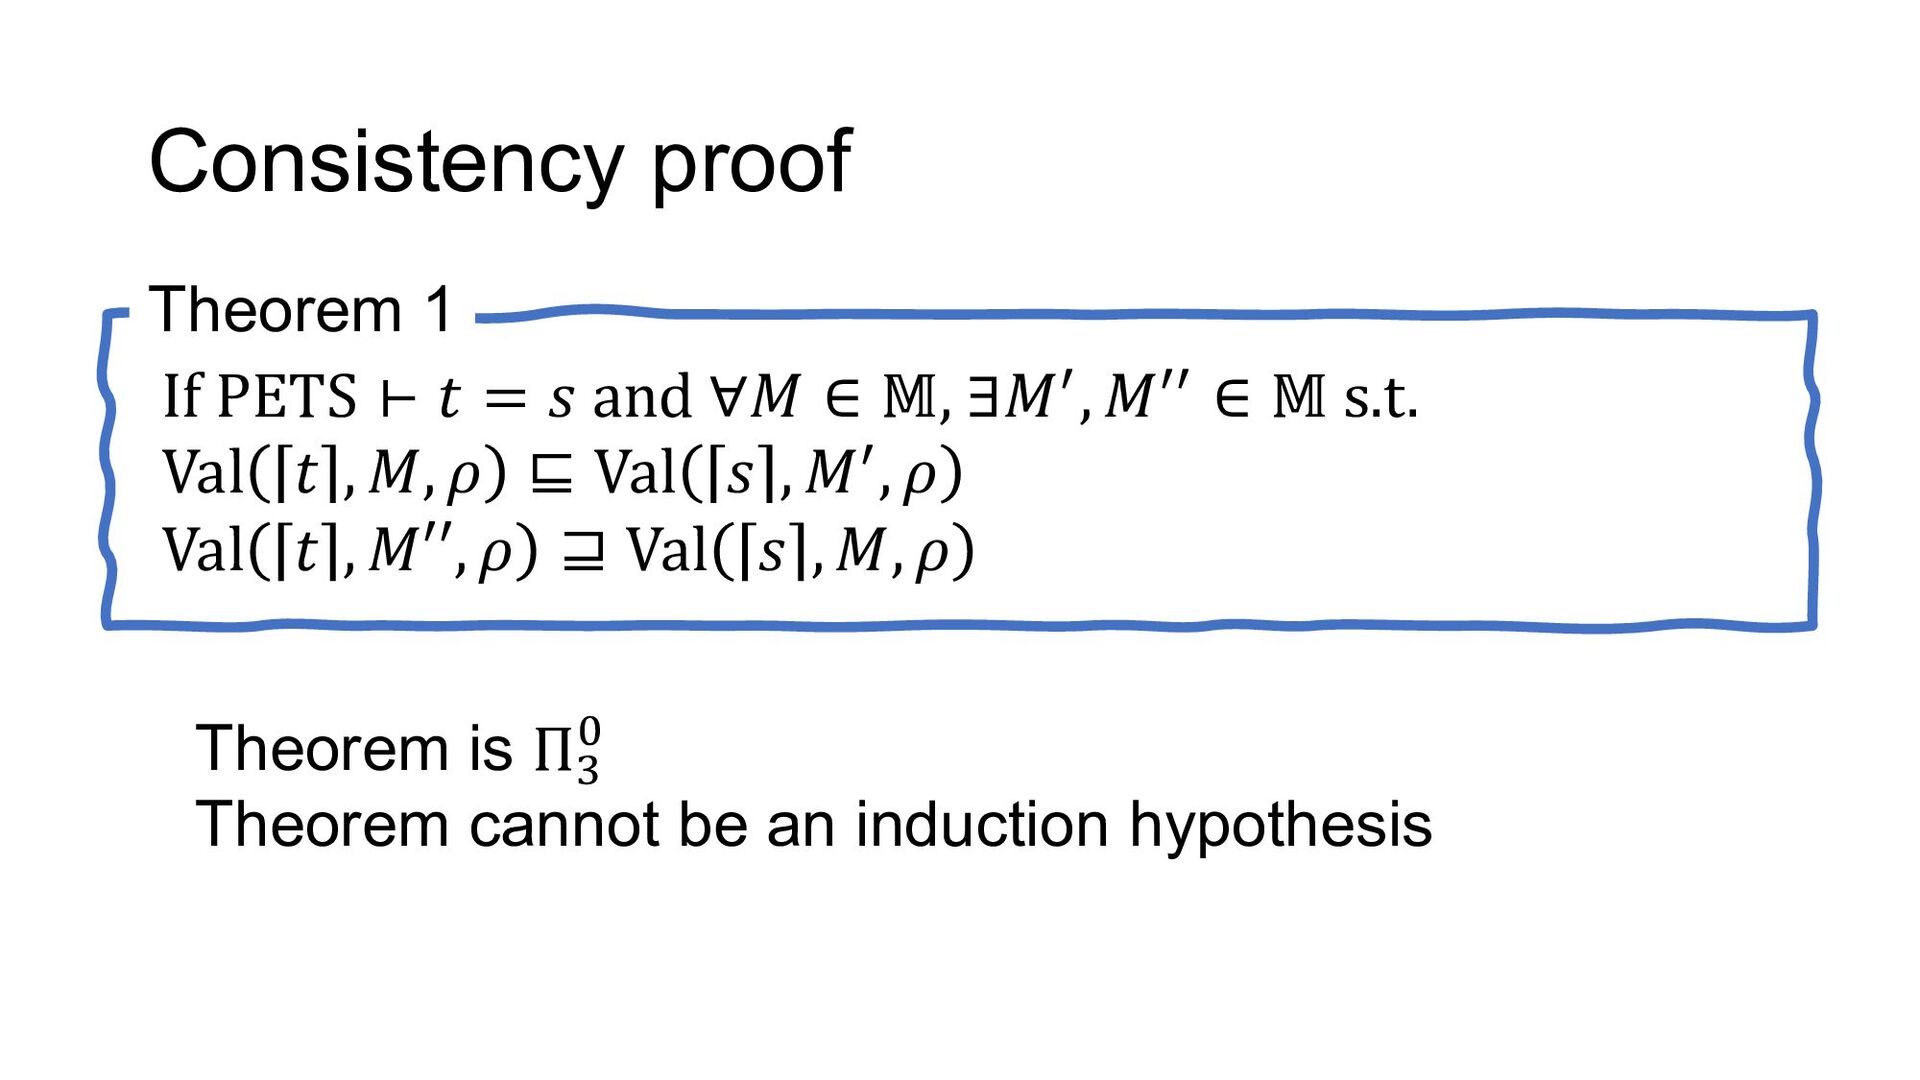
  23. Consistency proof Theorem 1 If PETS ⊢ 𝑡 = 𝑠

    and ∀𝑀 ∈ 𝕄, ∃𝑀(, 𝑀(( ∈ 𝕄 s.t. Val 𝑡 , 𝑀, 𝜌 ⊑ Val 𝑠 , 𝑀(, 𝜌 Val 𝑡 , 𝑀′′, 𝜌 ⊒ Val 𝑠 , 𝑀, 𝜌 Theorem is Π) * Theorem cannot be an induction hypothesis
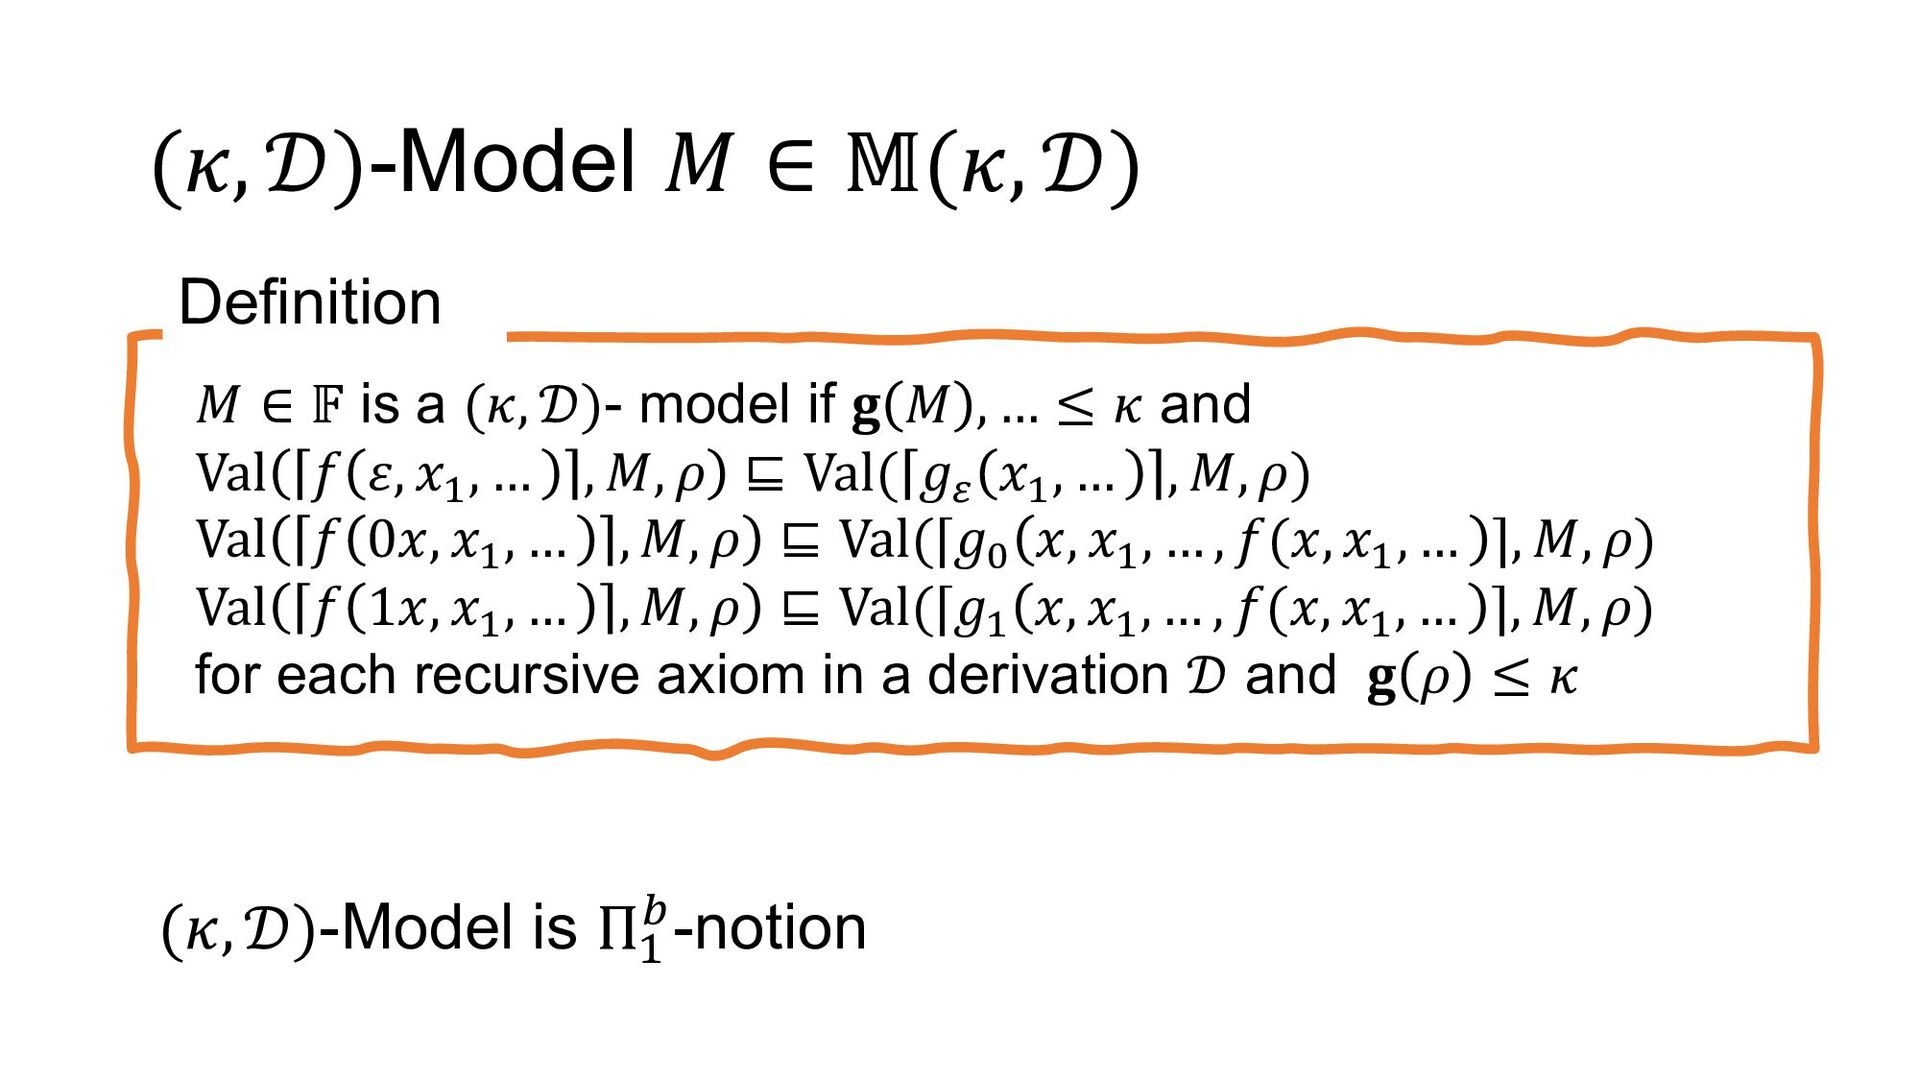
  24. (𝜅, 𝒟)-Model 𝑀 ∈ 𝕄(𝜅, 𝒟) 𝑀 ∈ 𝔽 is

    a (𝜅, 𝒟)- model if 𝐠 𝑀 , … ≤ 𝜅 and Val 𝑓 𝜀, 𝑥# , … , 𝑀, 𝜌 ⊑ Val( 𝑔A 𝑥# , … , 𝑀, 𝜌) Val 𝑓 0𝑥, 𝑥# , … , 𝑀, 𝜌 ⊑ Val(⌈𝑔B 𝑥, 𝑥# , … , 𝑓(𝑥, 𝑥# , … ⌉, 𝑀, 𝜌) Val 𝑓 1𝑥, 𝑥# , … , 𝑀, 𝜌 ⊑ Val(⌈𝑔# 𝑥, 𝑥# , … , 𝑓(𝑥, 𝑥# , … ⌉, 𝑀, 𝜌) for each recursive axiom in a derivation 𝒟 and 𝐠 𝜌 ≤ 𝜅 Definition (𝜅, 𝒟)-Model is Π# %-notion
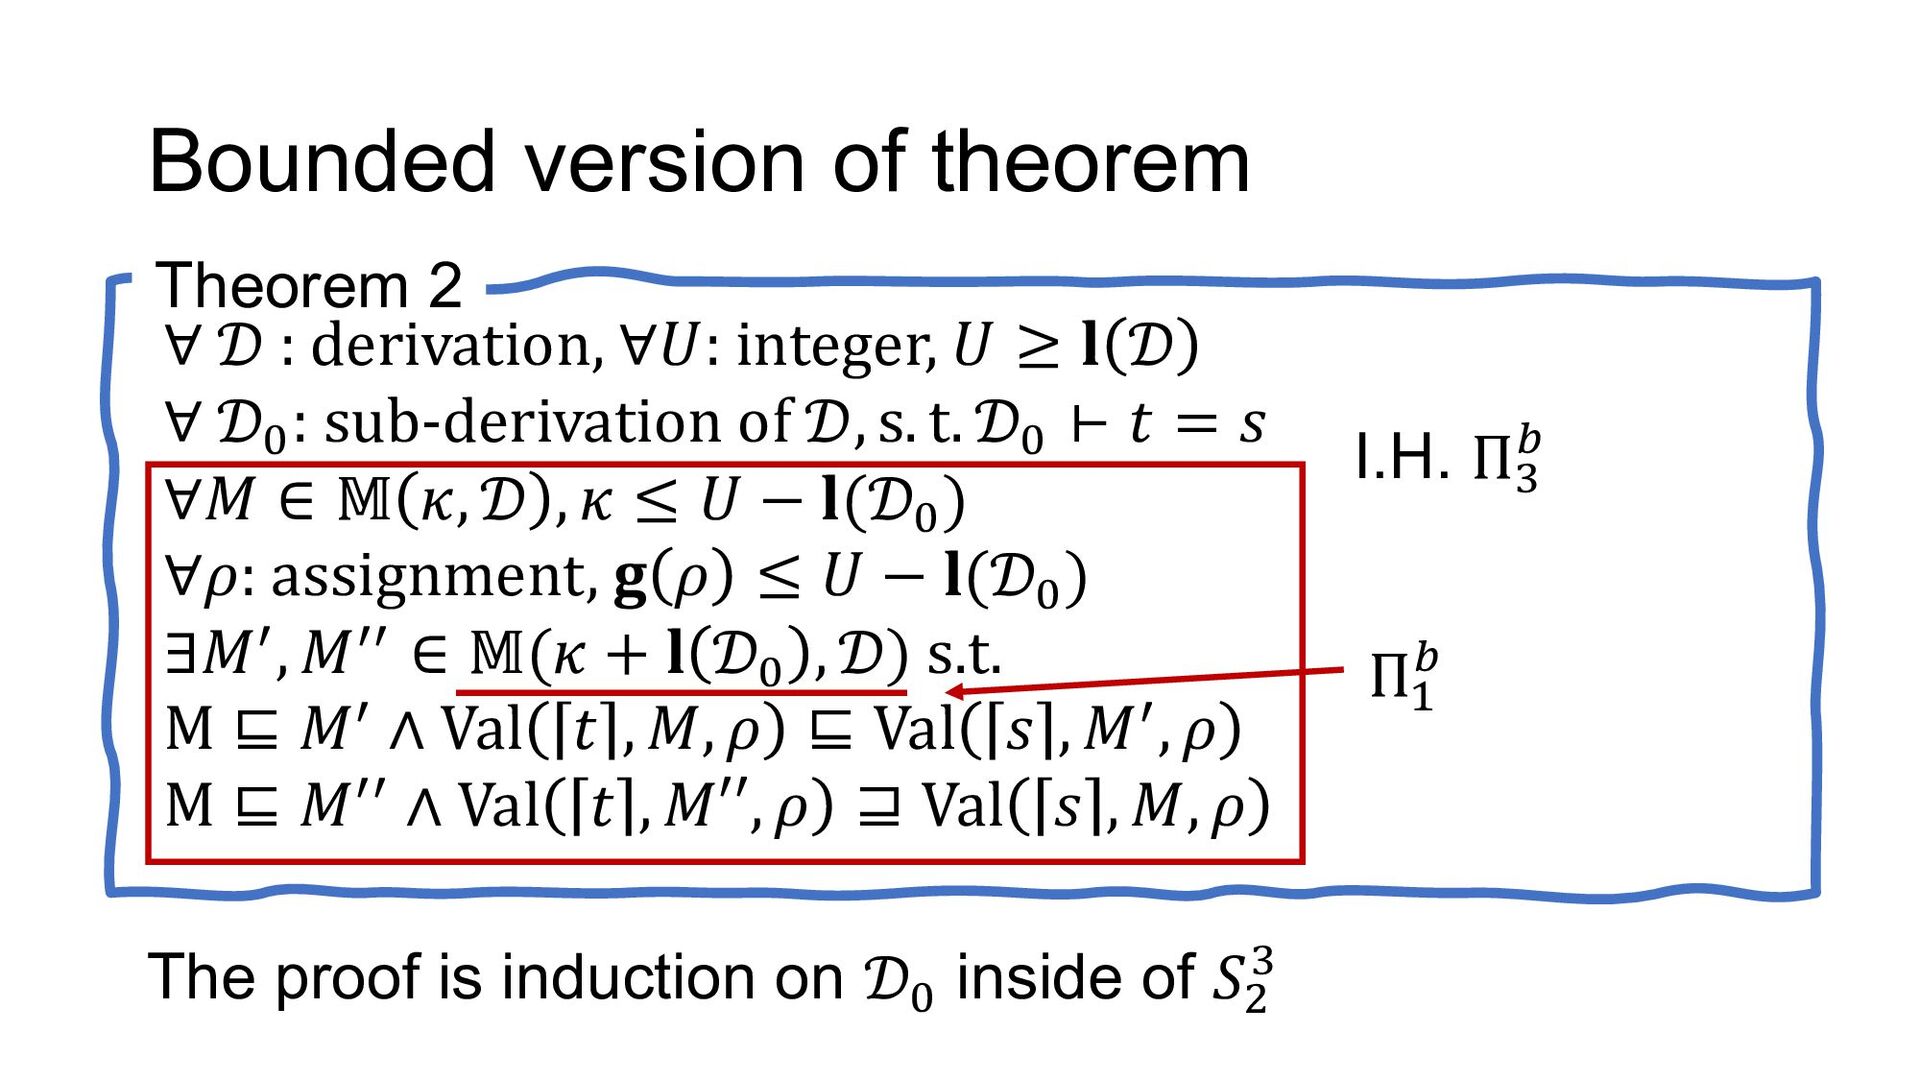
  25. Bounded version of theorem Theorem 2 ∀ 𝒟 : derivation,

    ∀𝑈: integer, 𝑈 ≥ 𝐥 𝒟 ∀ 𝒟* : sub-derivation of 𝒟, s. t. 𝒟* ⊢ 𝑡 = 𝑠 ∀𝑀 ∈ 𝕄 𝜅, 𝒟 , 𝜅 ≤ 𝑈 − 𝐥(𝒟* ) ∀𝜌: assignment, 𝐠 𝜌 ≤ 𝑈 − 𝐥(𝒟* ) ∃𝑀(, 𝑀(( ∈ 𝕄(𝜅 + 𝐥 𝒟* , 𝒟) s.t. M ⊑ 𝑀( ∧ Val 𝑡 , 𝑀, 𝜌 ⊑ Val 𝑠 , 𝑀(, 𝜌 M ⊑ 𝑀(( ∧ Val 𝑡 , 𝑀′′, 𝜌 ⊒ Val 𝑠 , 𝑀, 𝜌 The proof is induction on 𝒟* inside of 𝑆" ) I.H. Π) % Π# %
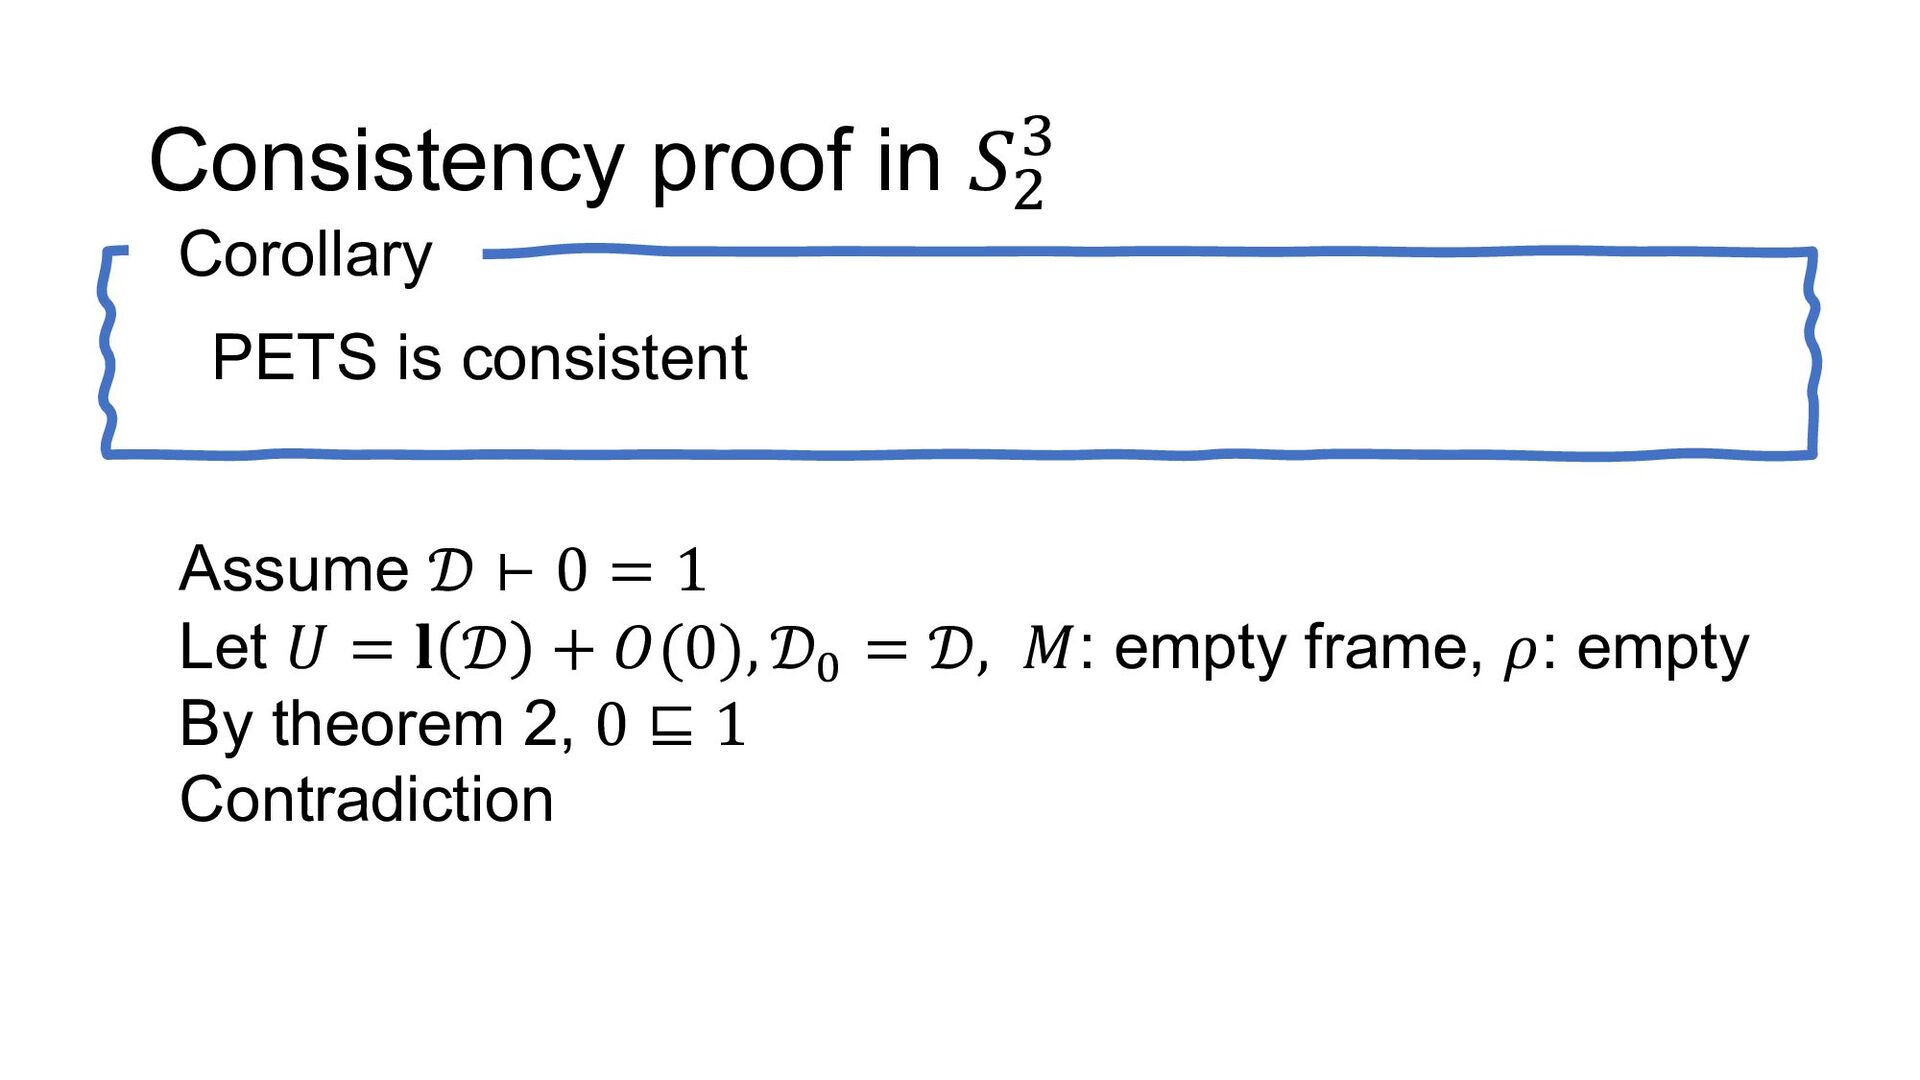
  26. Consistency proof in 𝑆2 † Corollary PETS is consistent Assume

    𝒟 ⊢ 0 = 1 Let 𝑈 = 𝐥 𝒟 + 𝑂(0), 𝒟* = 𝒟, 𝑀: empty frame, 𝜌: empty By theorem 2, 0 ⊑ 1 Contradiction
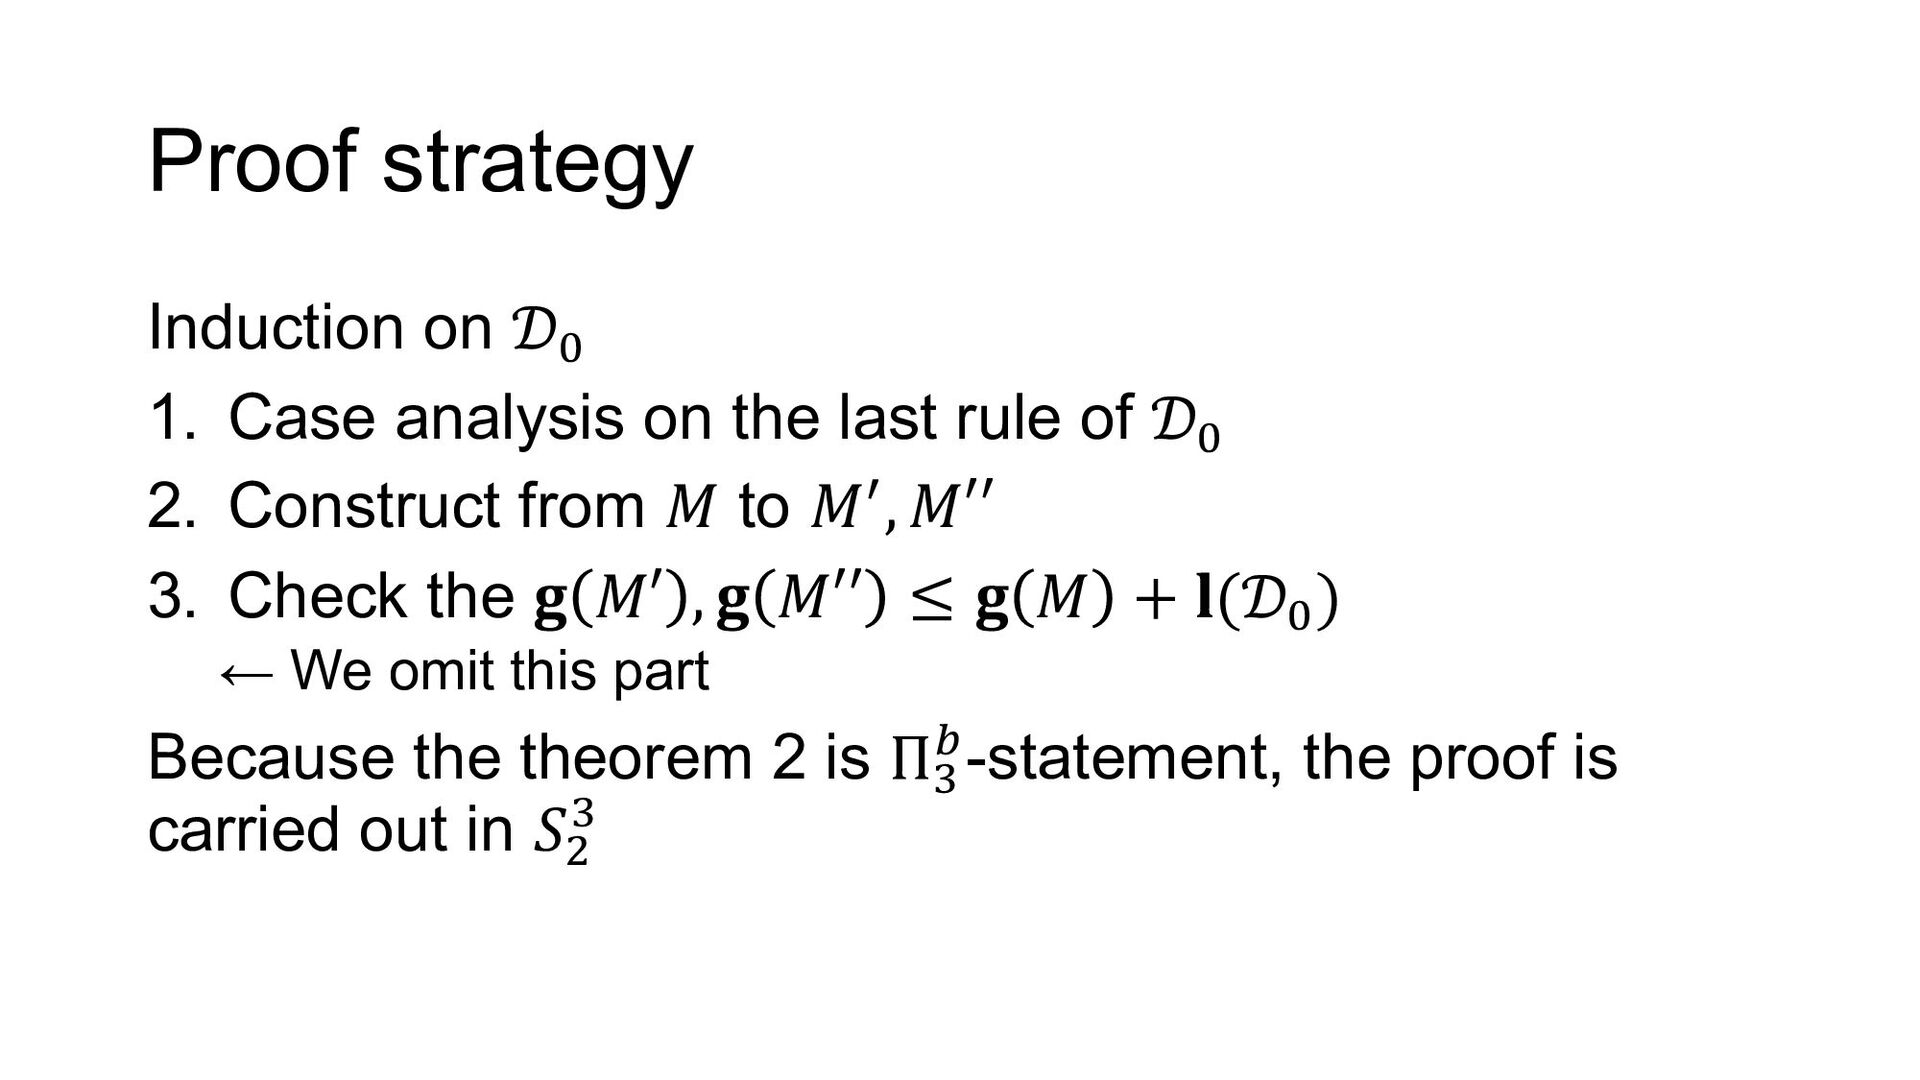
  27. Proof strategy Induction on 𝒟* 1. Case analysis on the

    last rule of 𝒟* 2. Construct from 𝑀 to 𝑀(, 𝑀′′ 3. Check the 𝐠 𝑀′ , 𝐠 𝑀′′ ≤ 𝐠 𝑀 + 𝐥(𝒟* ) ← We omit this part Because the theorem 2 is Π) %-statement, the proof is carried out in 𝑆" )
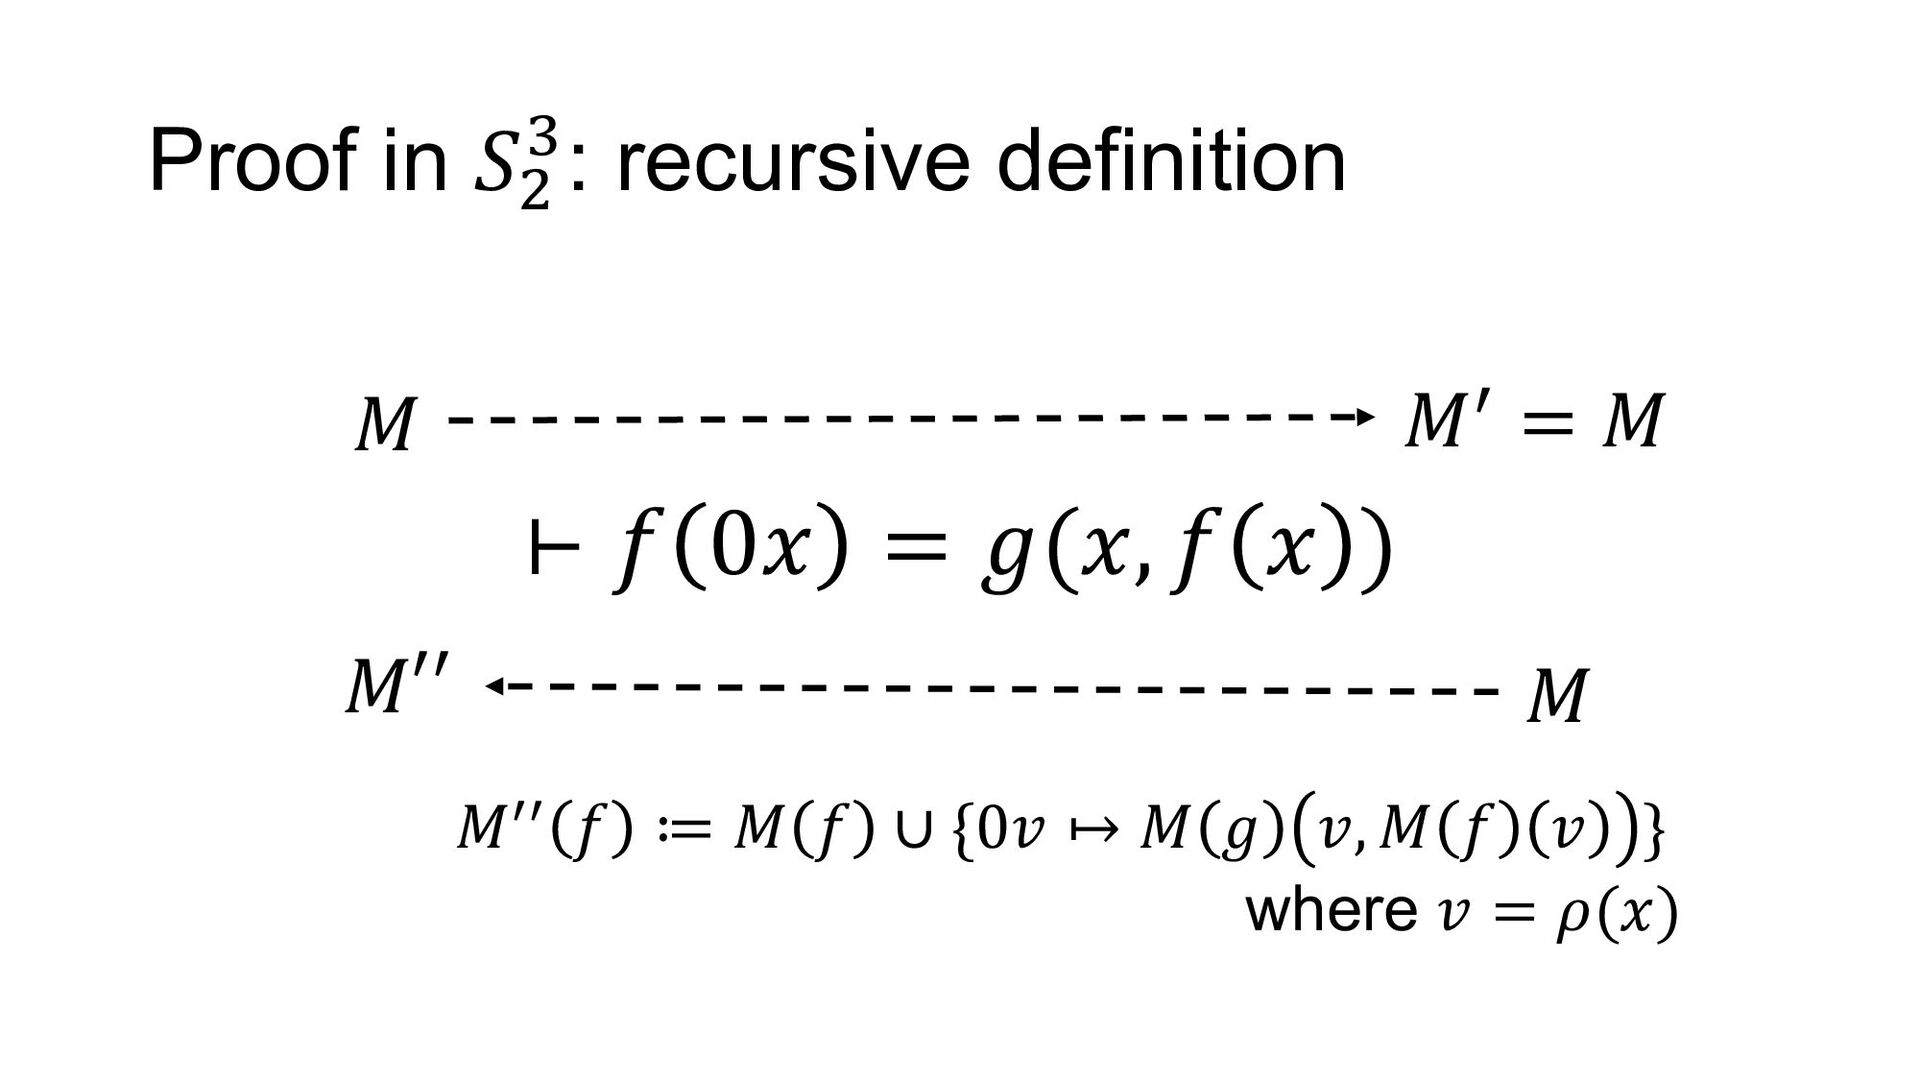
  28. Proof in 𝑆2 †: recursive definition ⊢ 𝑓 0𝑥 =

    𝑔(𝑥, 𝑓 𝑥 ) 𝑀 𝑀′′ 𝑀(( 𝑓 ≔ 𝑀 𝑓 ∪ {0𝑣 ↦ 𝑀 𝑔 𝑣, 𝑀 𝑓 𝑣 } where 𝑣 = 𝜌(𝑥) 𝑀 𝑀# = 𝑀
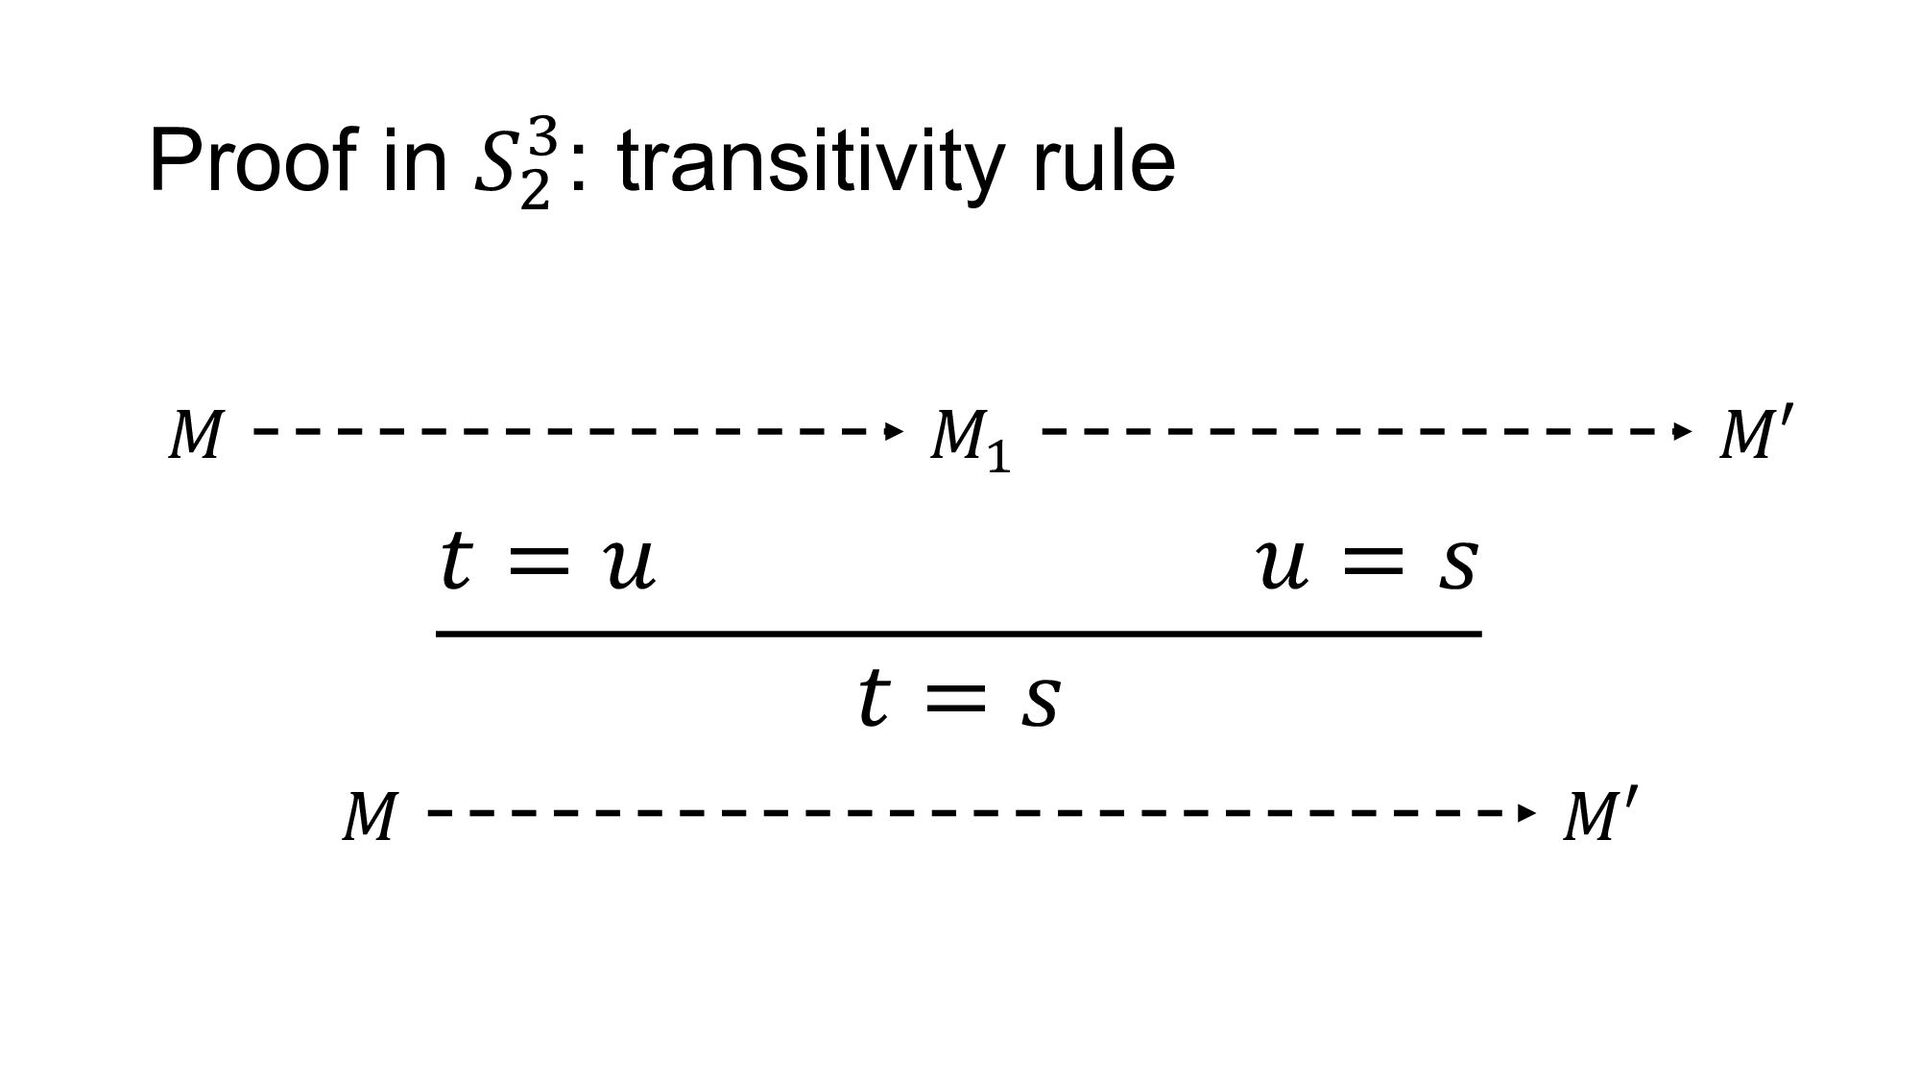
  29. Proof in 𝑆2 †: transitivity rule 𝑡 = 𝑢 𝑢

    = 𝑠 𝑡 = 𝑠 𝑀 𝑀! 𝑀′ 𝑀 𝑀′
  30. Proof in 𝑆2 † : compatibility rule 𝑡 = 𝑢

    𝑠 𝑡 = 𝑠 𝑢 𝑀 𝑀′ 𝑀 𝑀′ Val 𝑠 𝑡 , 𝑀, 𝜌 = Val 𝑠 𝑥 , 𝑀, 𝜌 𝑥 ↦ Val 𝑡 , 𝑀, 𝜌 ⊑ Val 𝑠 𝑥 , 𝑀, 𝜌 𝑥 ↦ Val 𝑢 , 𝑀E, 𝜌 ⊑ Val 𝑠 𝑢 , 𝑀E, 𝜌
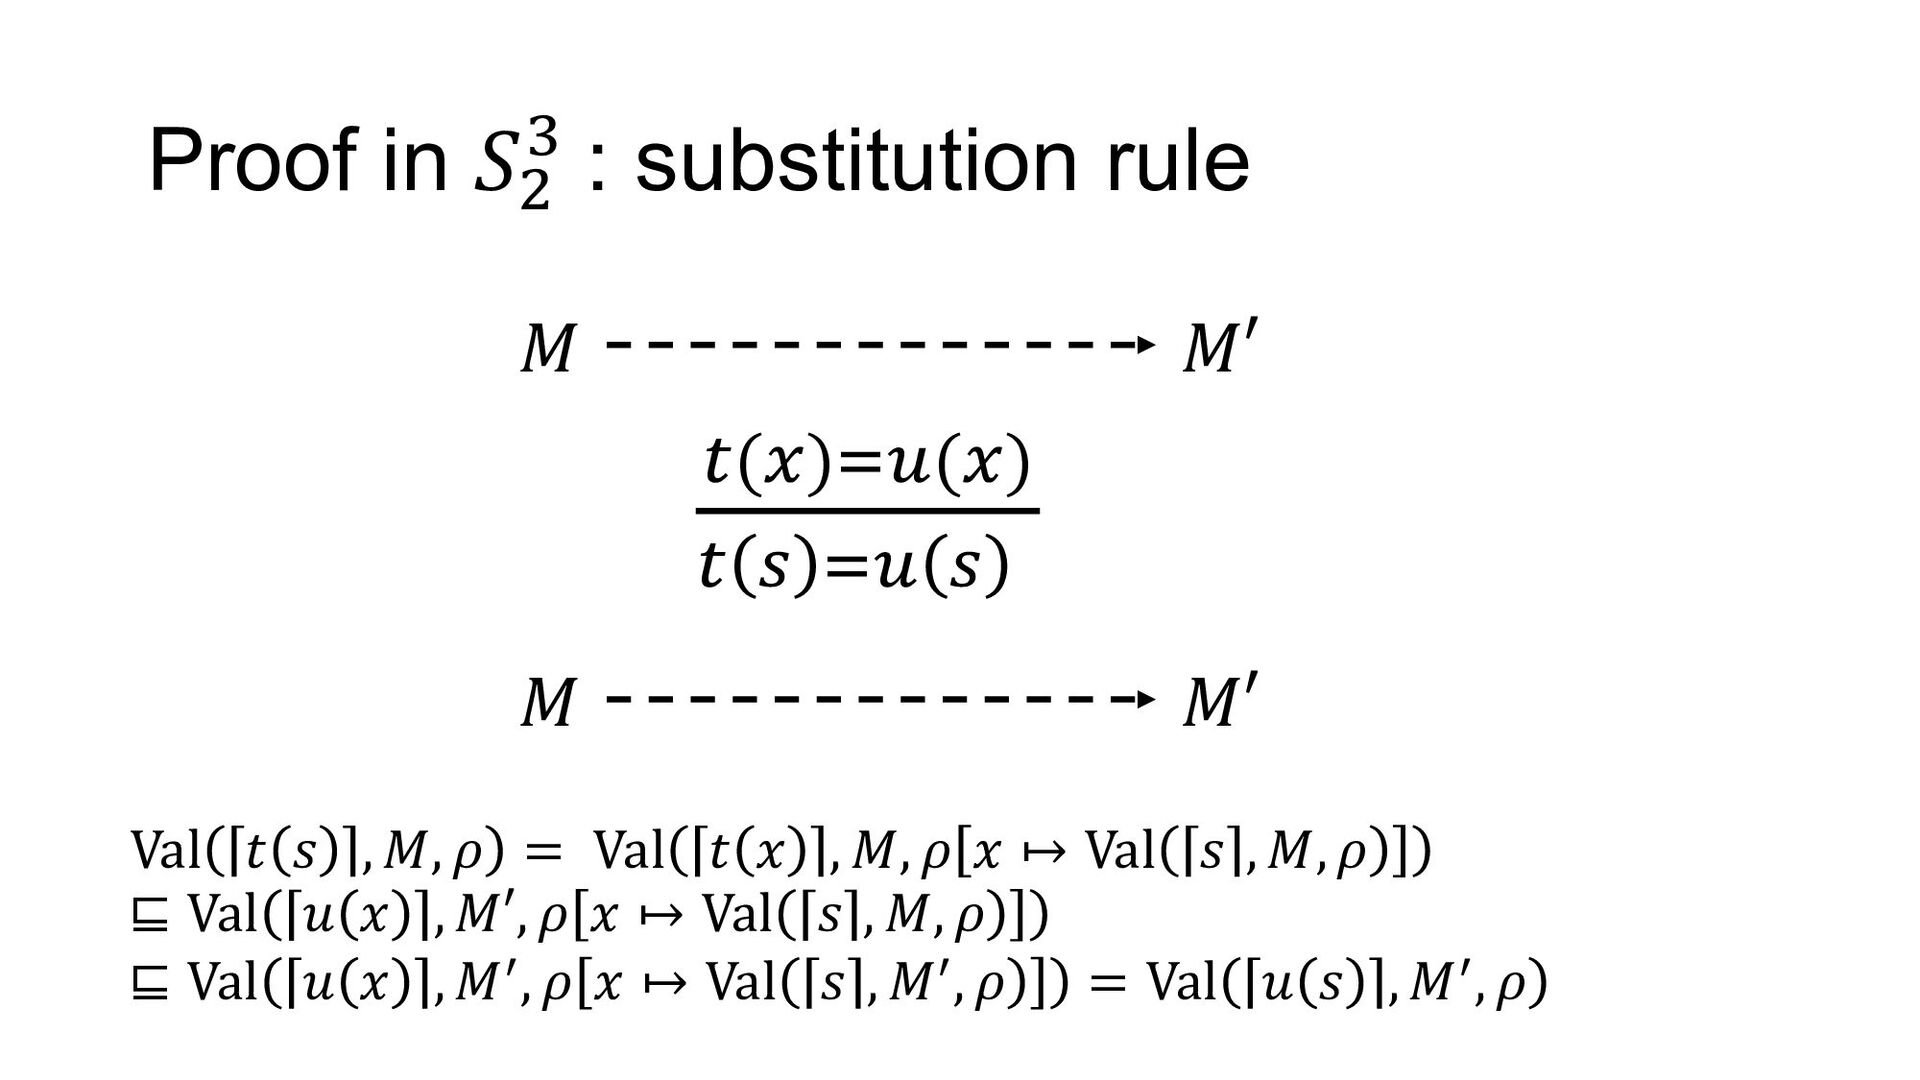
  31. Proof in 𝑆2 † : substitution rule !(#)%&(#) ! '

    %& ' 𝑀 𝑀′ 𝑀 𝑀′ Val 𝑡 𝑠 , 𝑀, 𝜌 = Val 𝑡 𝑥 , 𝑀, 𝜌 𝑥 ↦ Val 𝑠 , 𝑀, 𝜌 ⊑ Val 𝑢 𝑥 , 𝑀′, 𝜌 𝑥 ↦ Val 𝑠 , 𝑀, 𝜌 ⊑ Val 𝑢 𝑥 , 𝑀E, 𝜌 𝑥 ↦ Val 𝑠 , 𝑀E, 𝜌 = Val 𝑢 𝑠 , 𝑀E, 𝜌
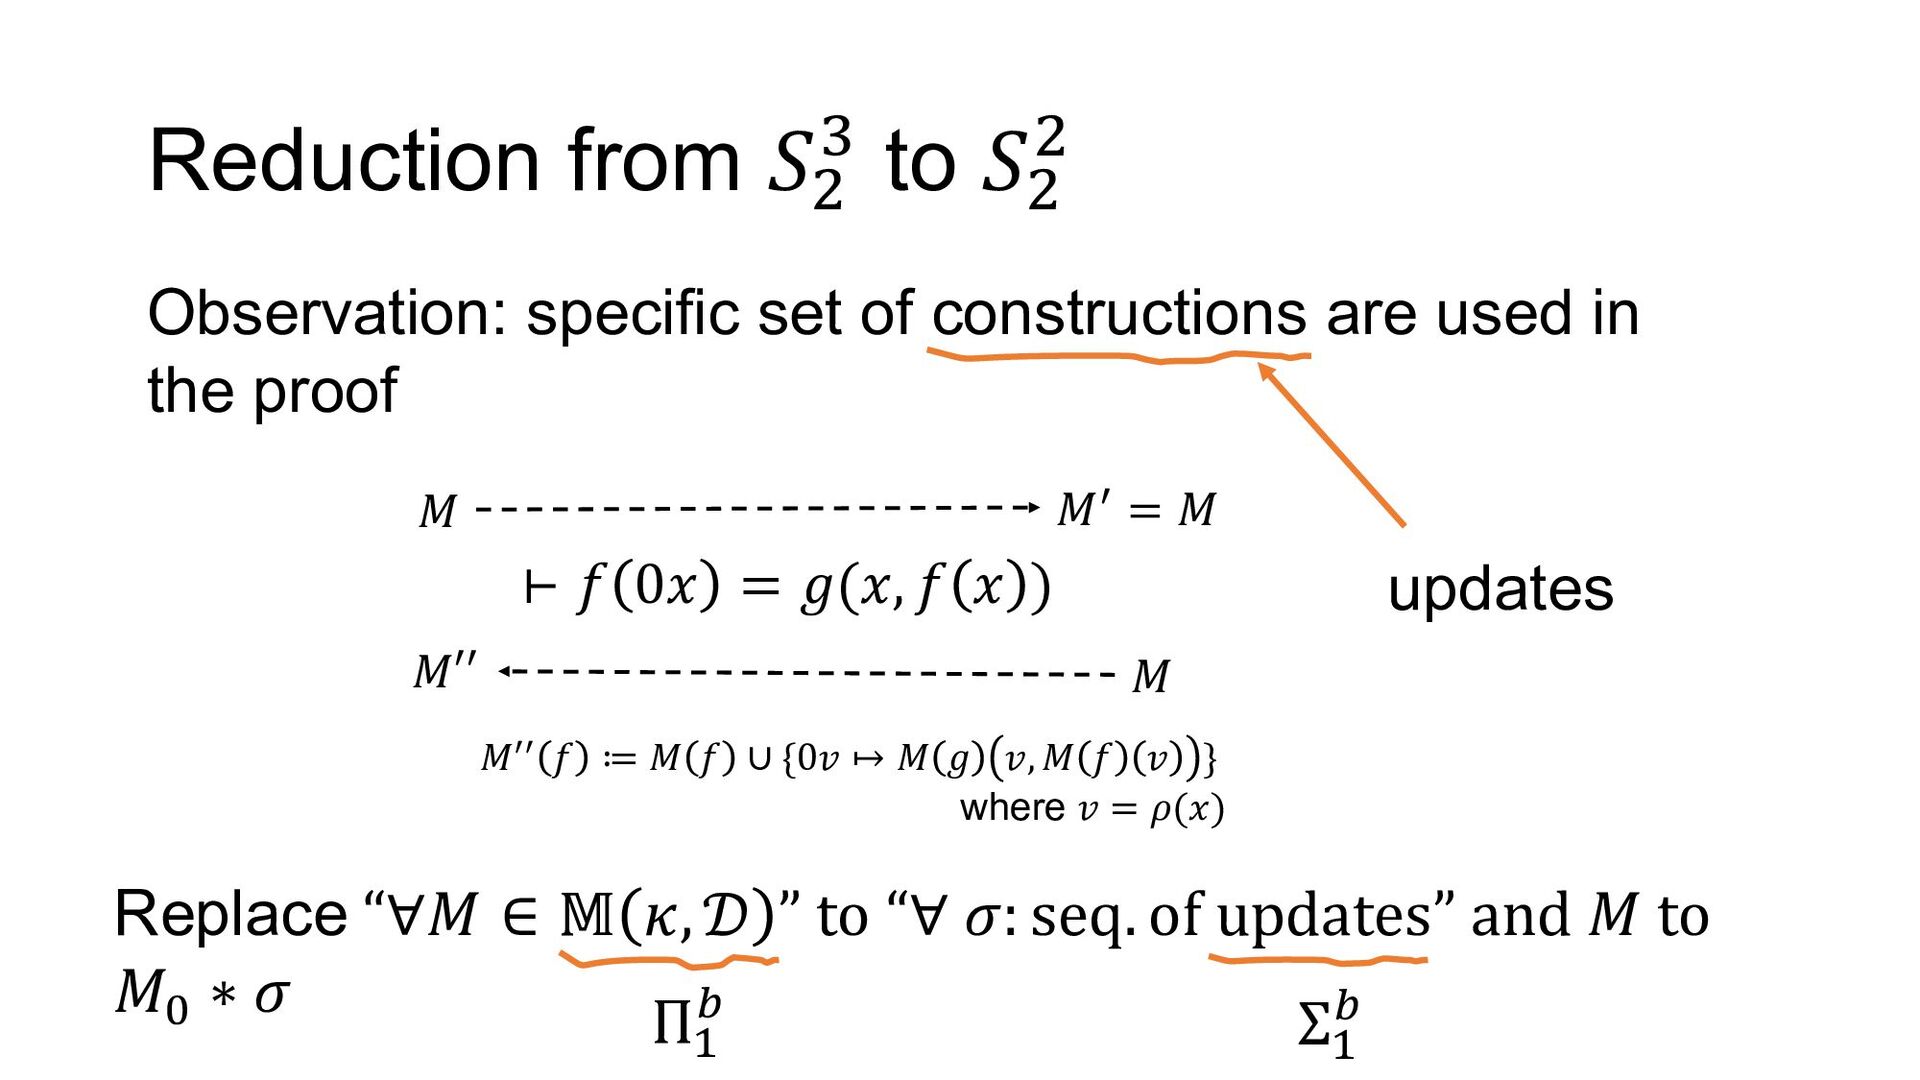
  32. Reduction from 𝑆2 † to 𝑆2 2 ⊢ " 0$

    = &($, " $ ) ! !′′ !!! " ≔ ! " ∪ {0' ↦ ! ) ', ! " ' } where ' = -(/) ! !! = ! Observation: specific set of constructions are used in the proof updates Replace “∀𝑀 ∈ 𝕄 𝜅, 𝒟 ” to “∀ 𝜎: seq. of updates” and 𝑀 to 𝑀* ∗ 𝜎 Π# % Σ# %
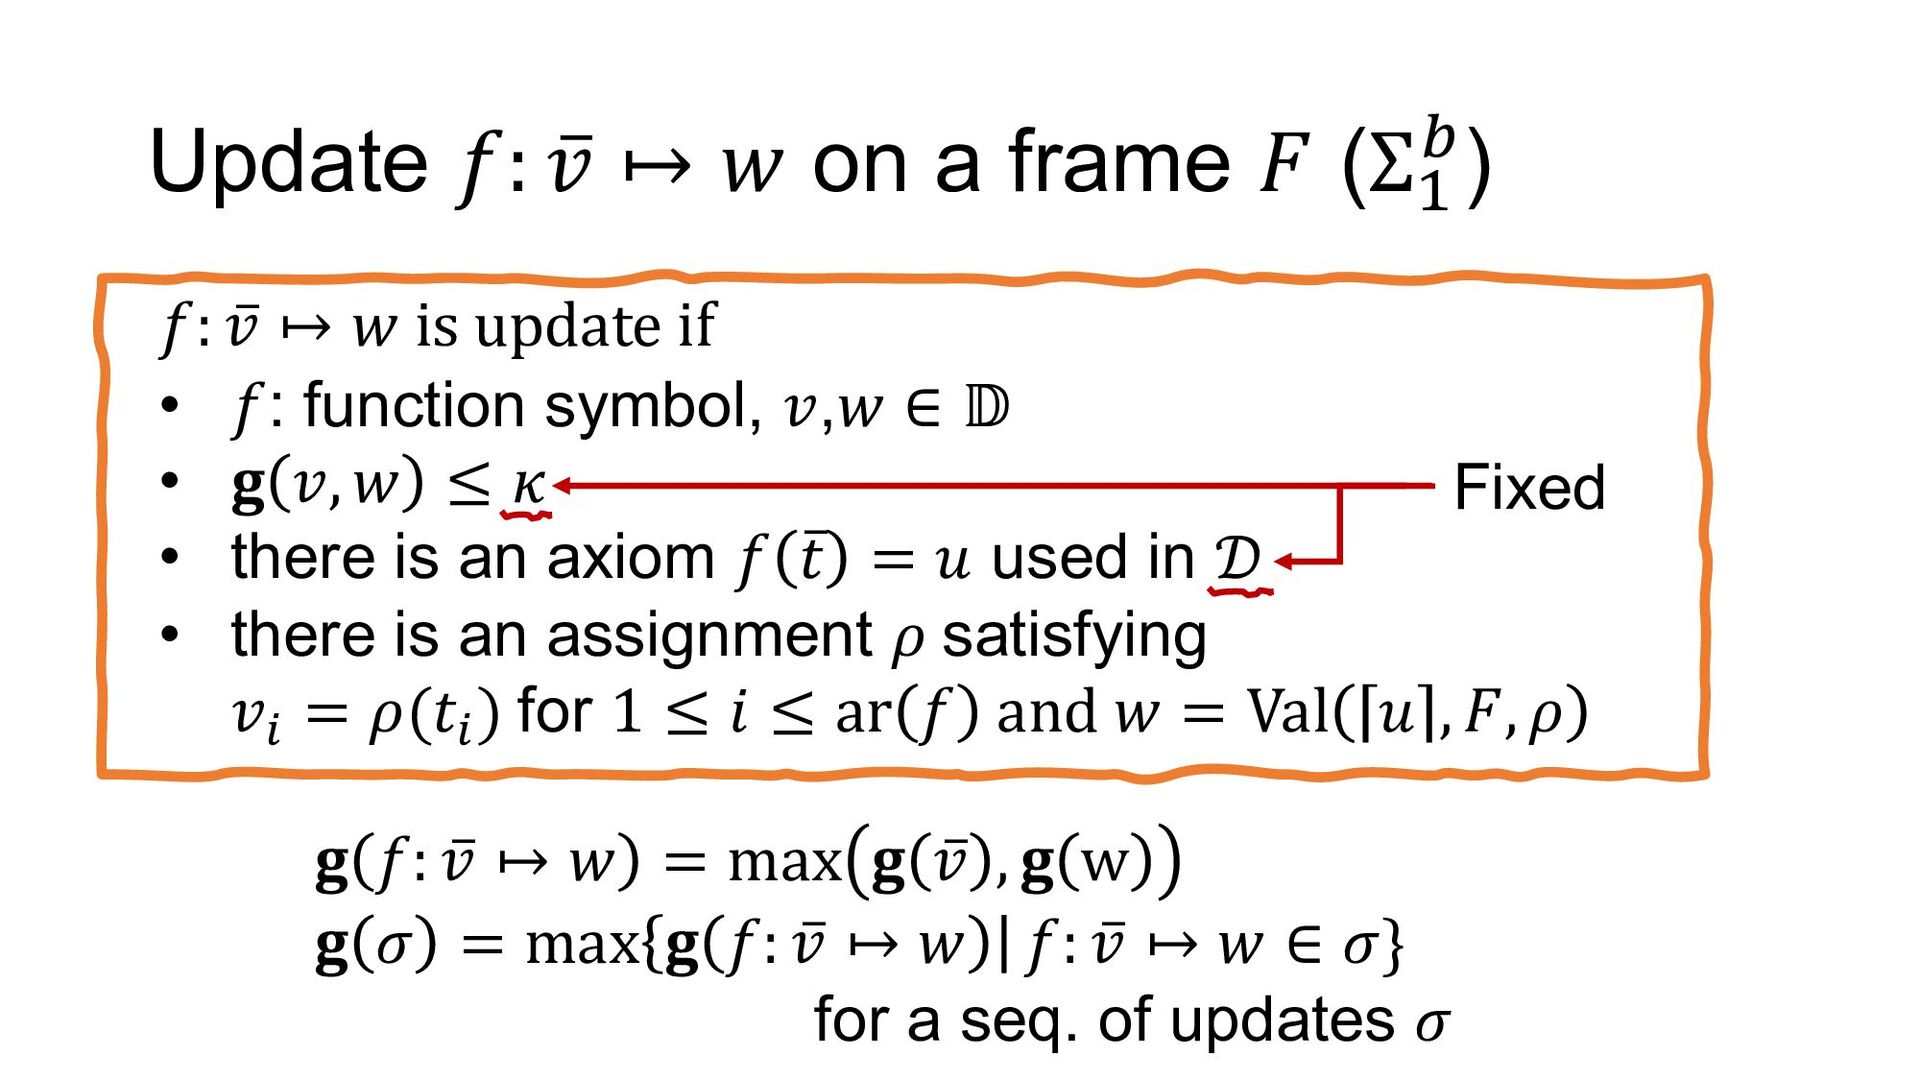
  33. Update 𝑓: ̅ 𝑣 ↦ 𝑤 on a frame 𝐹

    (Σ` Ž) 𝑓: ̅ 𝑣 ↦ 𝑤 is update if • 𝑓: function symbol, 𝑣,𝑤 ∈ 𝔻 • 𝐠 𝑣, 𝑤 ≤ 𝜅 • there is an axiom 𝑓 ̅ 𝑡 = 𝑢 used in 𝒟 • there is an assignment 𝜌 satisfying 𝑣& = 𝜌(𝑡& ) for 1 ≤ 𝑖 ≤ ar 𝑓 and 𝑤 = Val 𝑢 , 𝐹, 𝜌 Fixed 𝐠 𝑓: ̅ 𝑣 ↦ 𝑤 = max 𝐠 ̅ 𝑣 , 𝐠 w 𝐠 𝜎 = max 𝐠 𝑓: ̅ 𝑣 ↦ 𝑤 𝑓: ̅ 𝑣 ↦ 𝑤 ∈ 𝜎} for a seq. of updates 𝜎
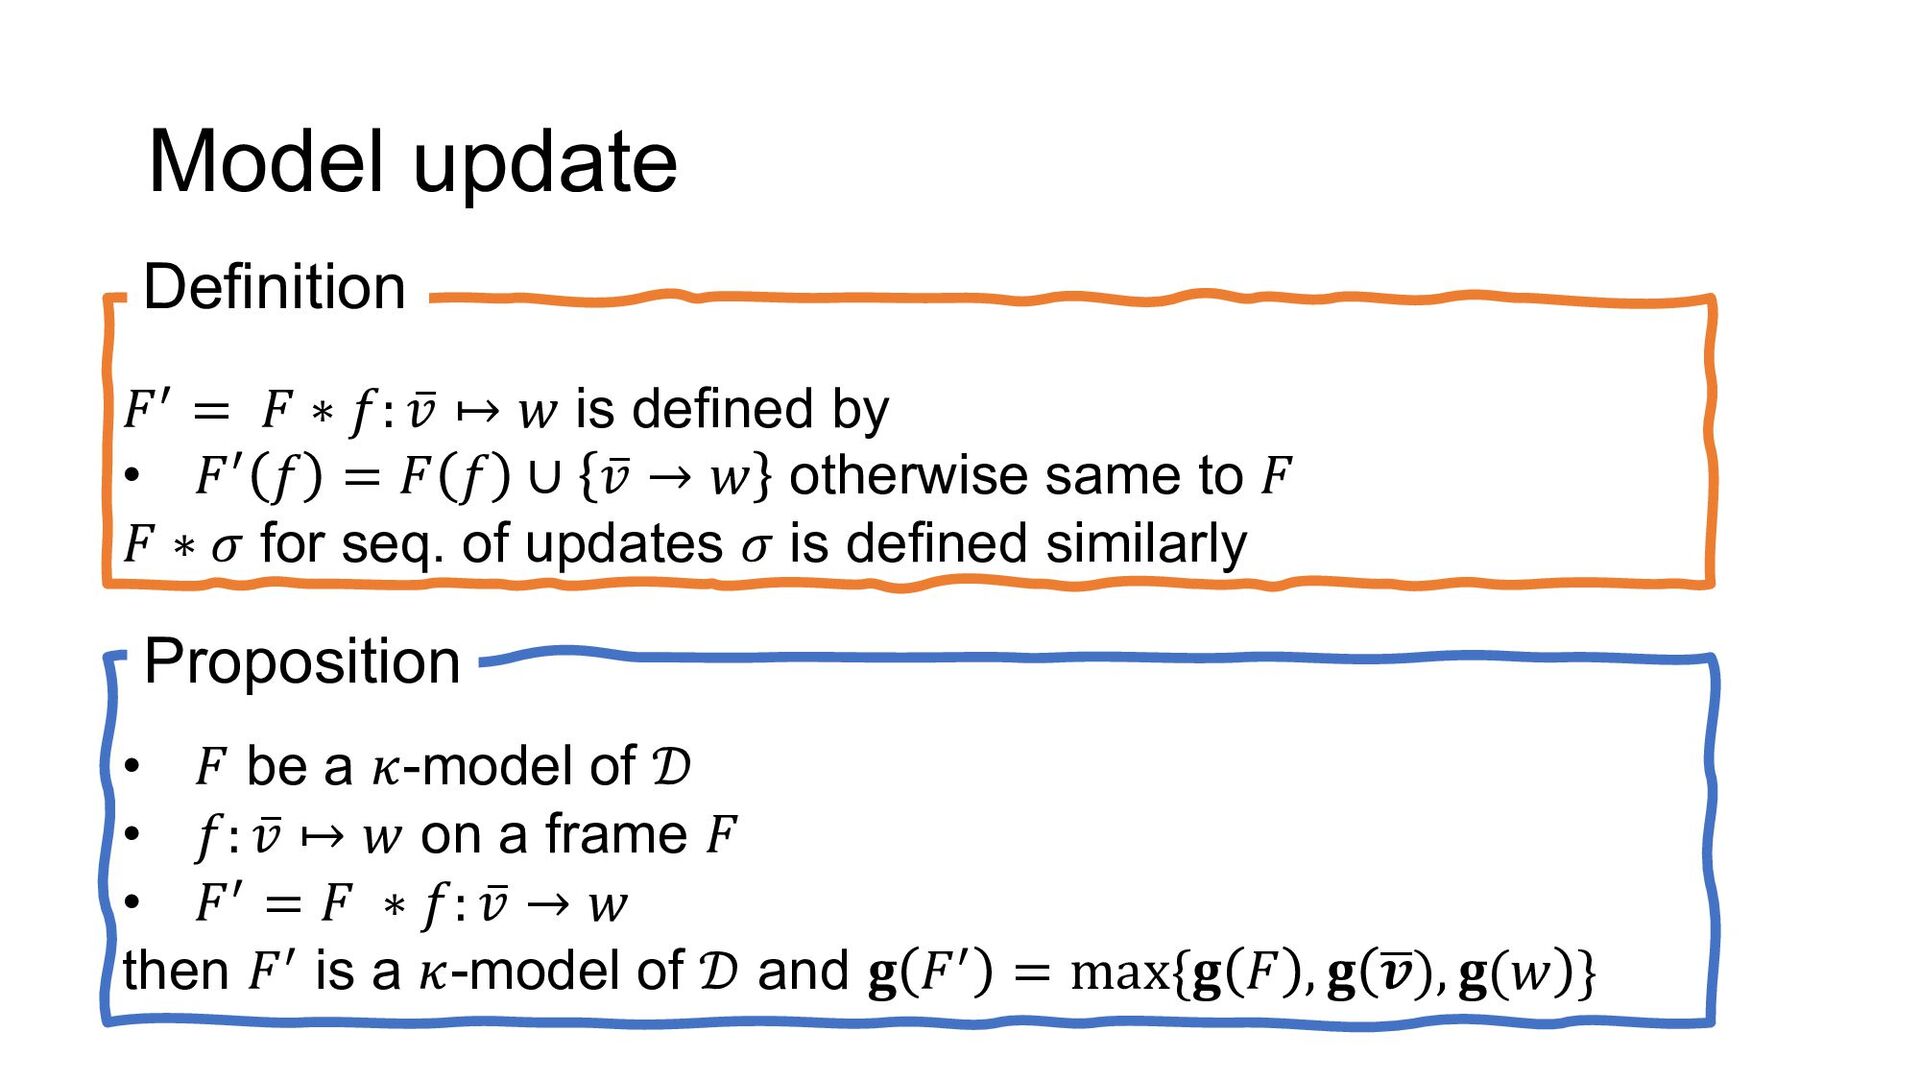
  34. • 𝐹 be a 𝜅-model of 𝒟 • 𝑓: ̅

    𝑣 ↦ 𝑤 on a frame 𝐹 • 𝐹E = 𝐹 ∗ 𝑓: ̅ 𝑣 → 𝑤 then 𝐹E is a 𝜅-model of 𝒟 and 𝐠 𝐹E = max{𝐠 𝐹 , 𝐠 y 𝒗), 𝐠(𝑤 } Proposition 𝐹E = 𝐹 ∗ 𝑓: ̅ 𝑣 ↦ 𝑤 is defined by • 𝐹E 𝑓 = 𝐹 𝑓 ∪ ̅ 𝑣 → 𝑤 otherwise same to 𝐹 𝐹 ∗ 𝜎 for seq. of updates 𝜎 is defined similarly Definition Model update
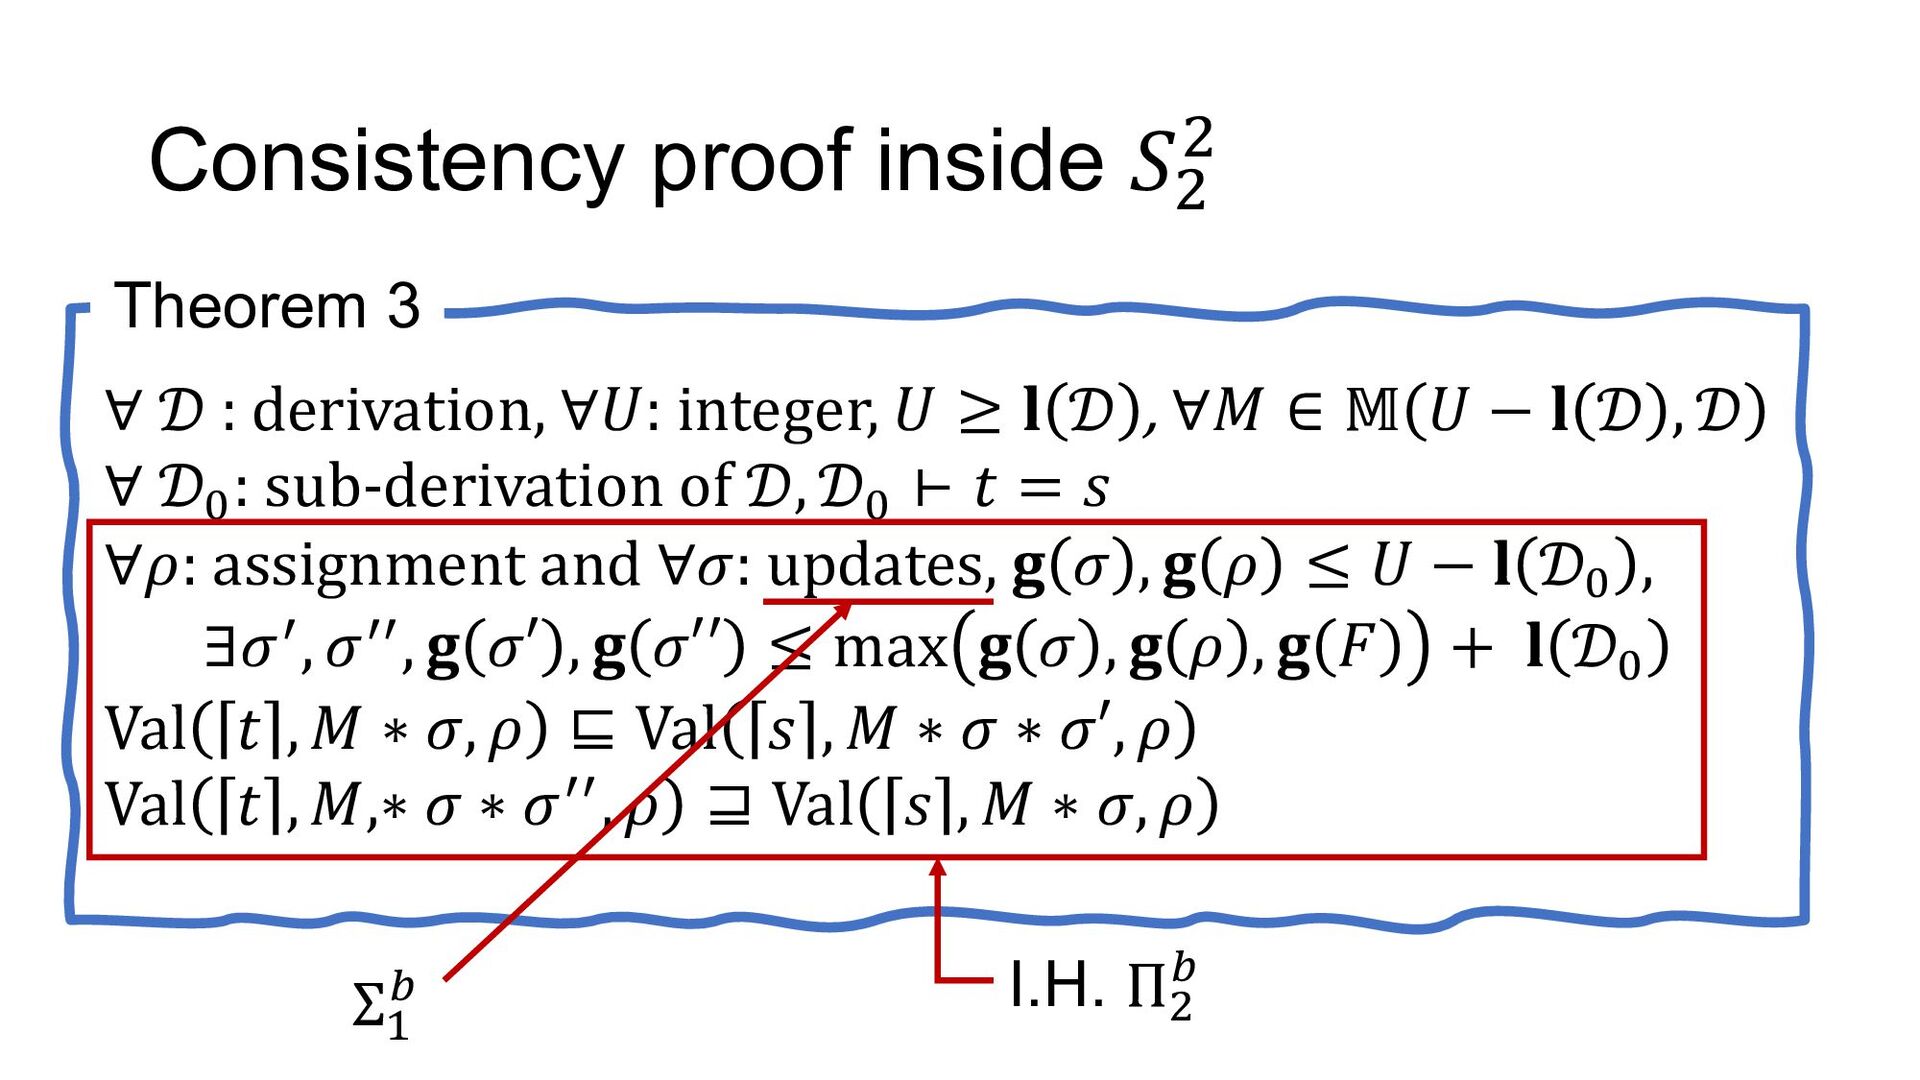
  35. Consistency proof inside 𝑆2 2 Theorem 3 ∀ 𝒟 :

    derivation, ∀𝑈: integer, 𝑈 ≥ 𝐥 𝒟 , ∀𝑀 ∈ 𝕄 𝑈 − 𝐥 𝒟 , 𝒟 ∀ 𝒟* : sub-derivation of 𝒟, 𝒟* ⊢ 𝑡 = 𝑠 ∀𝜌: assignment and ∀𝜎: updates, 𝐠 𝜎 , 𝐠 𝜌 ≤ 𝑈 − 𝐥 𝒟* , ∃𝜎(, 𝜎((, 𝐠 𝜎′ , 𝐠 𝜎′′ ≤ max 𝐠 𝜎 , 𝐠 𝜌 , 𝐠 𝐹 + 𝐥 𝒟* Val 𝑡 , 𝑀 ∗ 𝜎, 𝜌 ⊑ Val 𝑠 , 𝑀 ∗ 𝜎 ∗ 𝜎′, 𝜌 Val 𝑡 , 𝑀,∗ 𝜎 ∗ 𝜎((, 𝜌 ⊒ Val 𝑠 , 𝑀 ∗ 𝜎, 𝜌 I.H. Π" % Σ# %
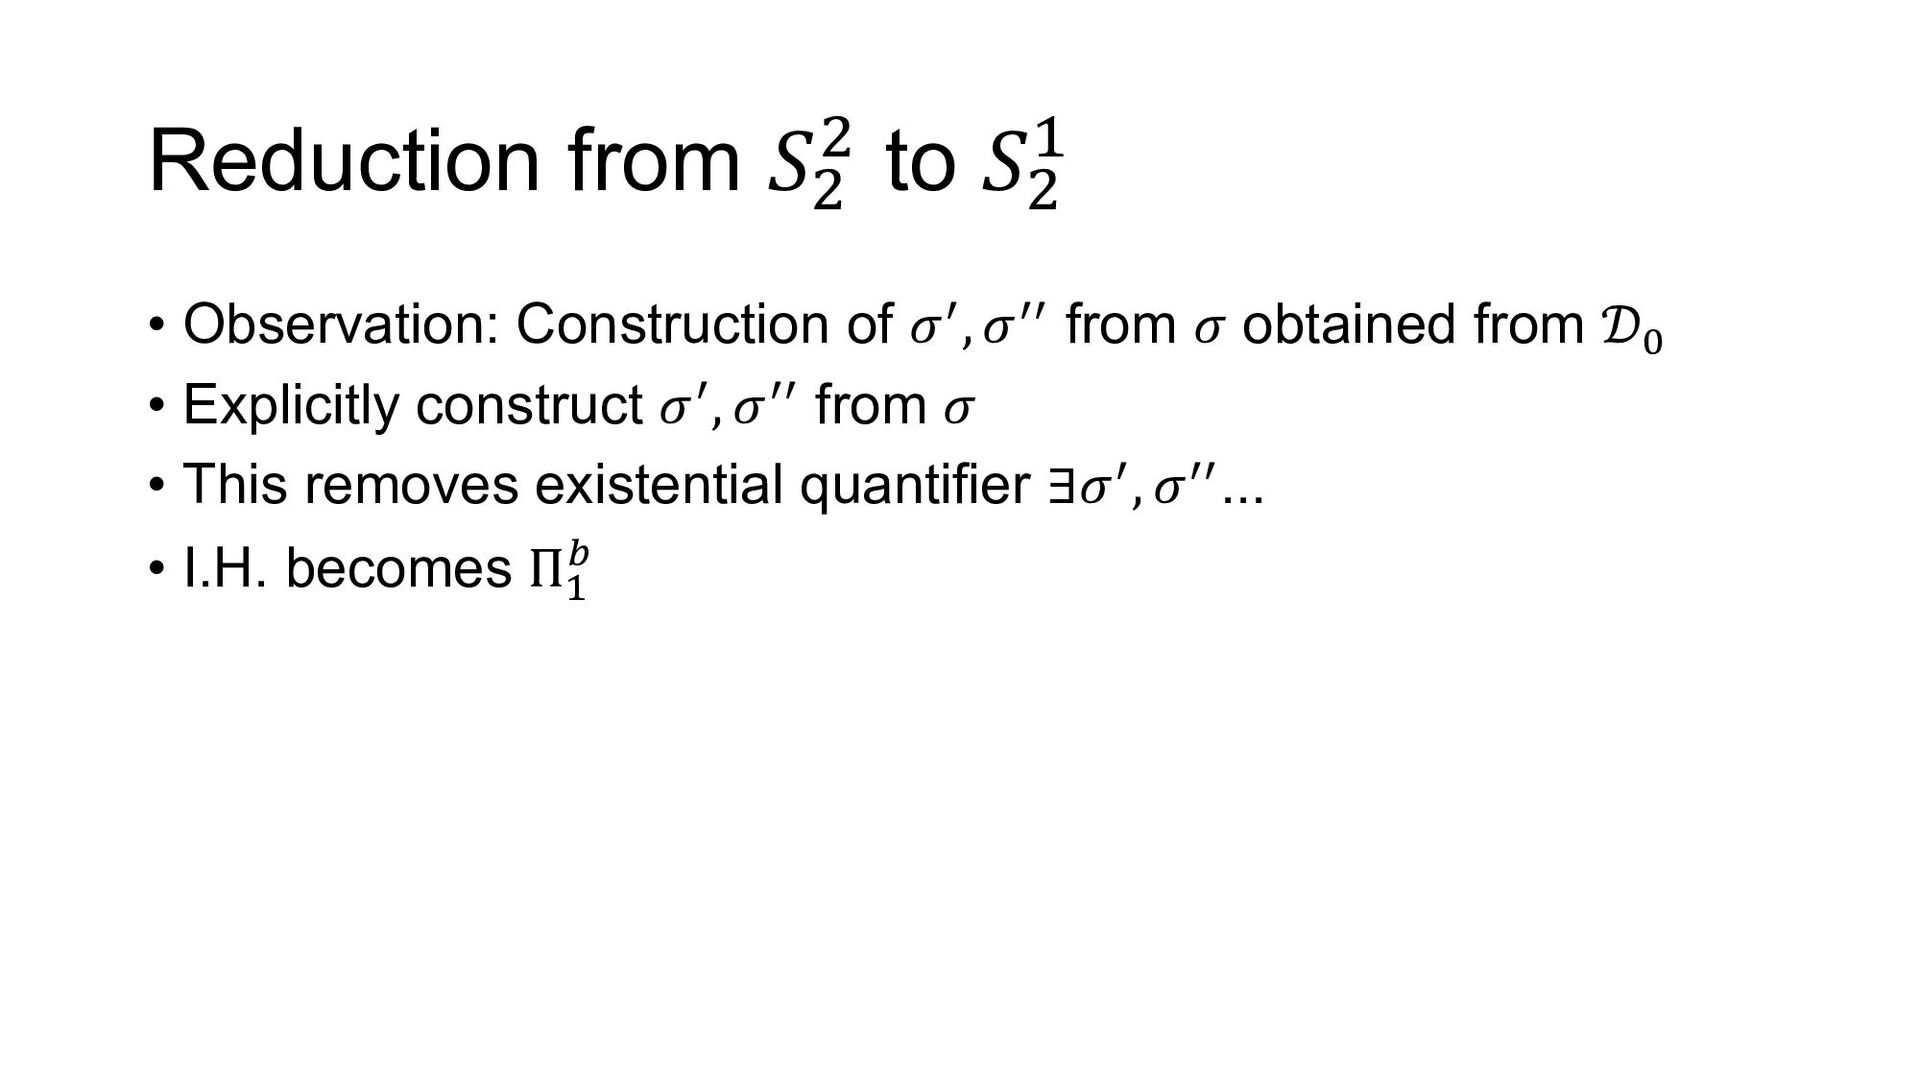
  36. Reduction from 𝑆2 2 to 𝑆2 ` • Observation: Construction

    of 𝜎E, 𝜎EE from 𝜎 obtained from 𝒟B • Explicitly construct 𝜎E, 𝜎EE from 𝜎 • This removes existential quantifier ∃𝜎E, 𝜎EE... • I.H. becomes Π# 1
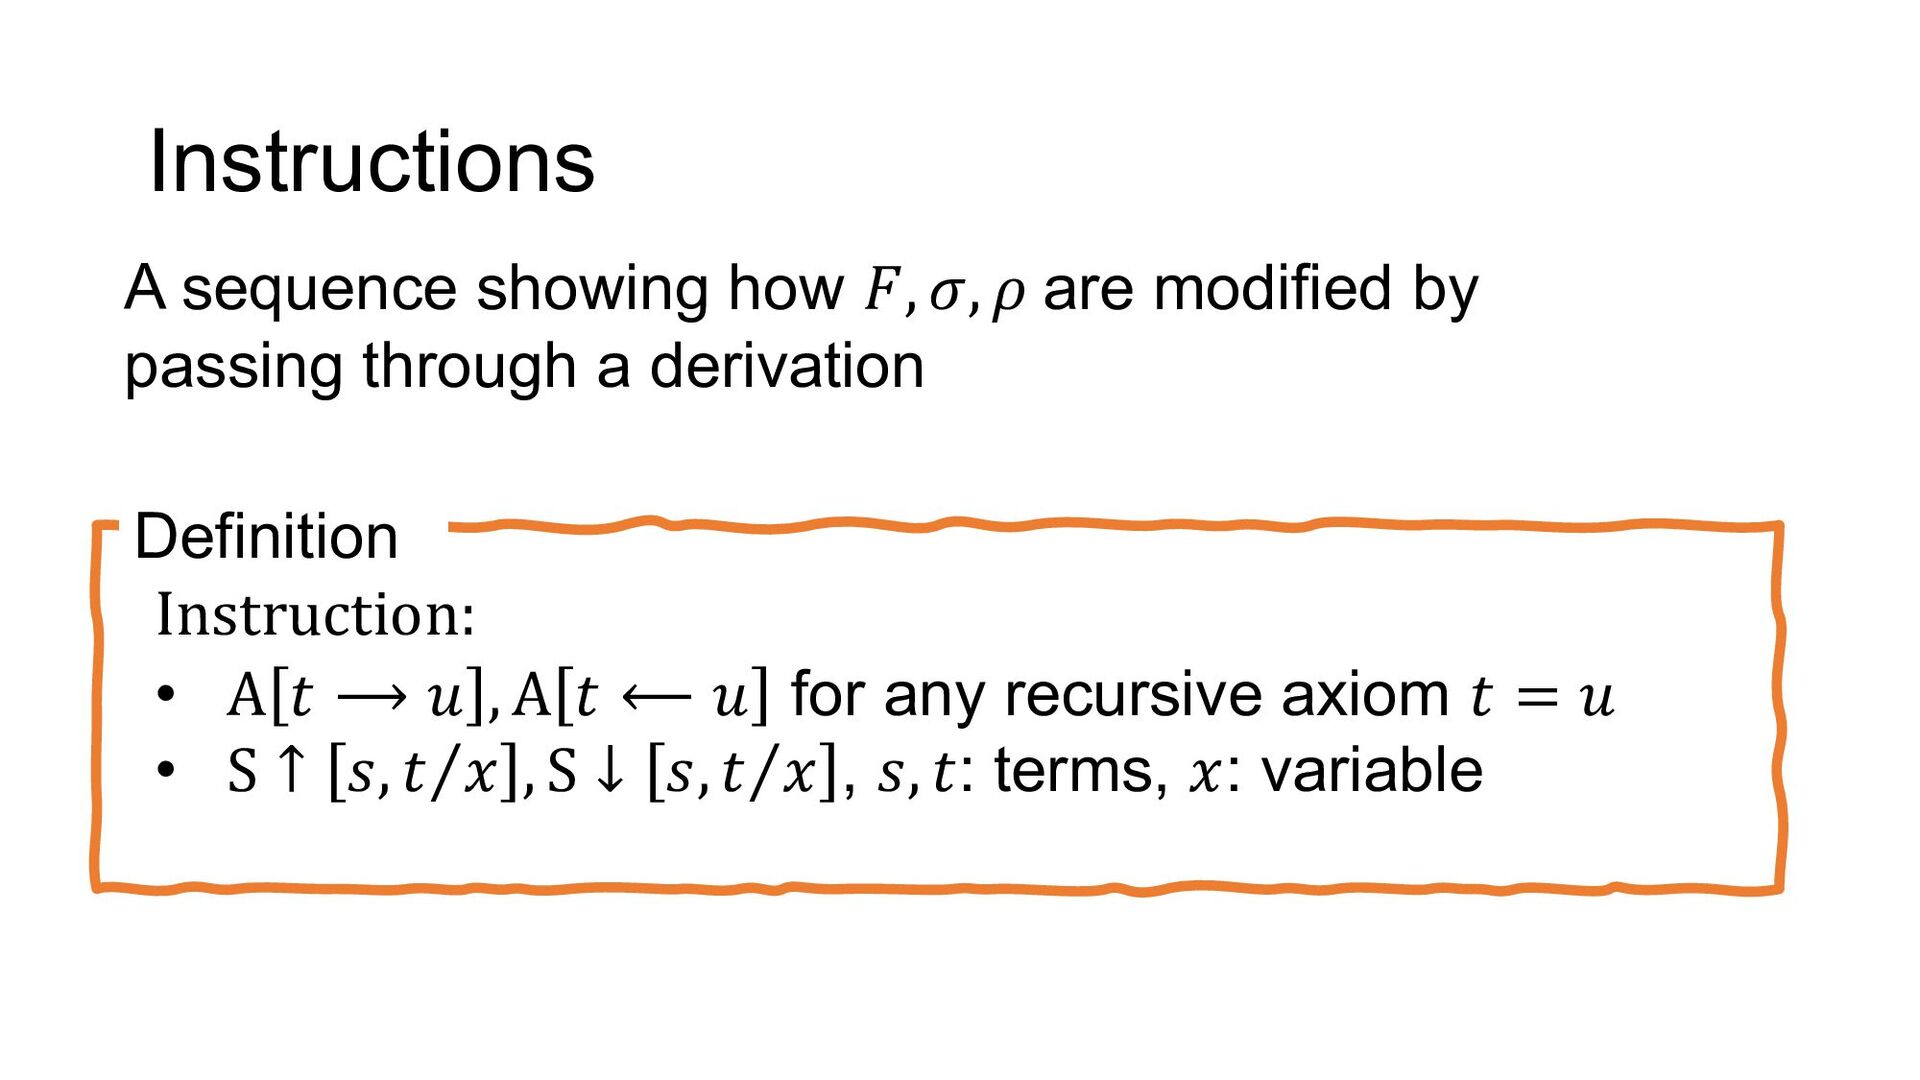
  37. Instructions A sequence showing how 𝐹, 𝜎, 𝜌 are modified

    by passing through a derivation Instruction: • A 𝑡 ⟶ 𝑢 , A 𝑡 ⟵ 𝑢 for any recursive axiom 𝑡 = 𝑢 • S ↑ 𝑠, ⁄ 𝑡 𝑥 , S ↓ 𝑠, ⁄ 𝑡 𝑥 , 𝑠, 𝑡: terms, 𝑥: variable Definition
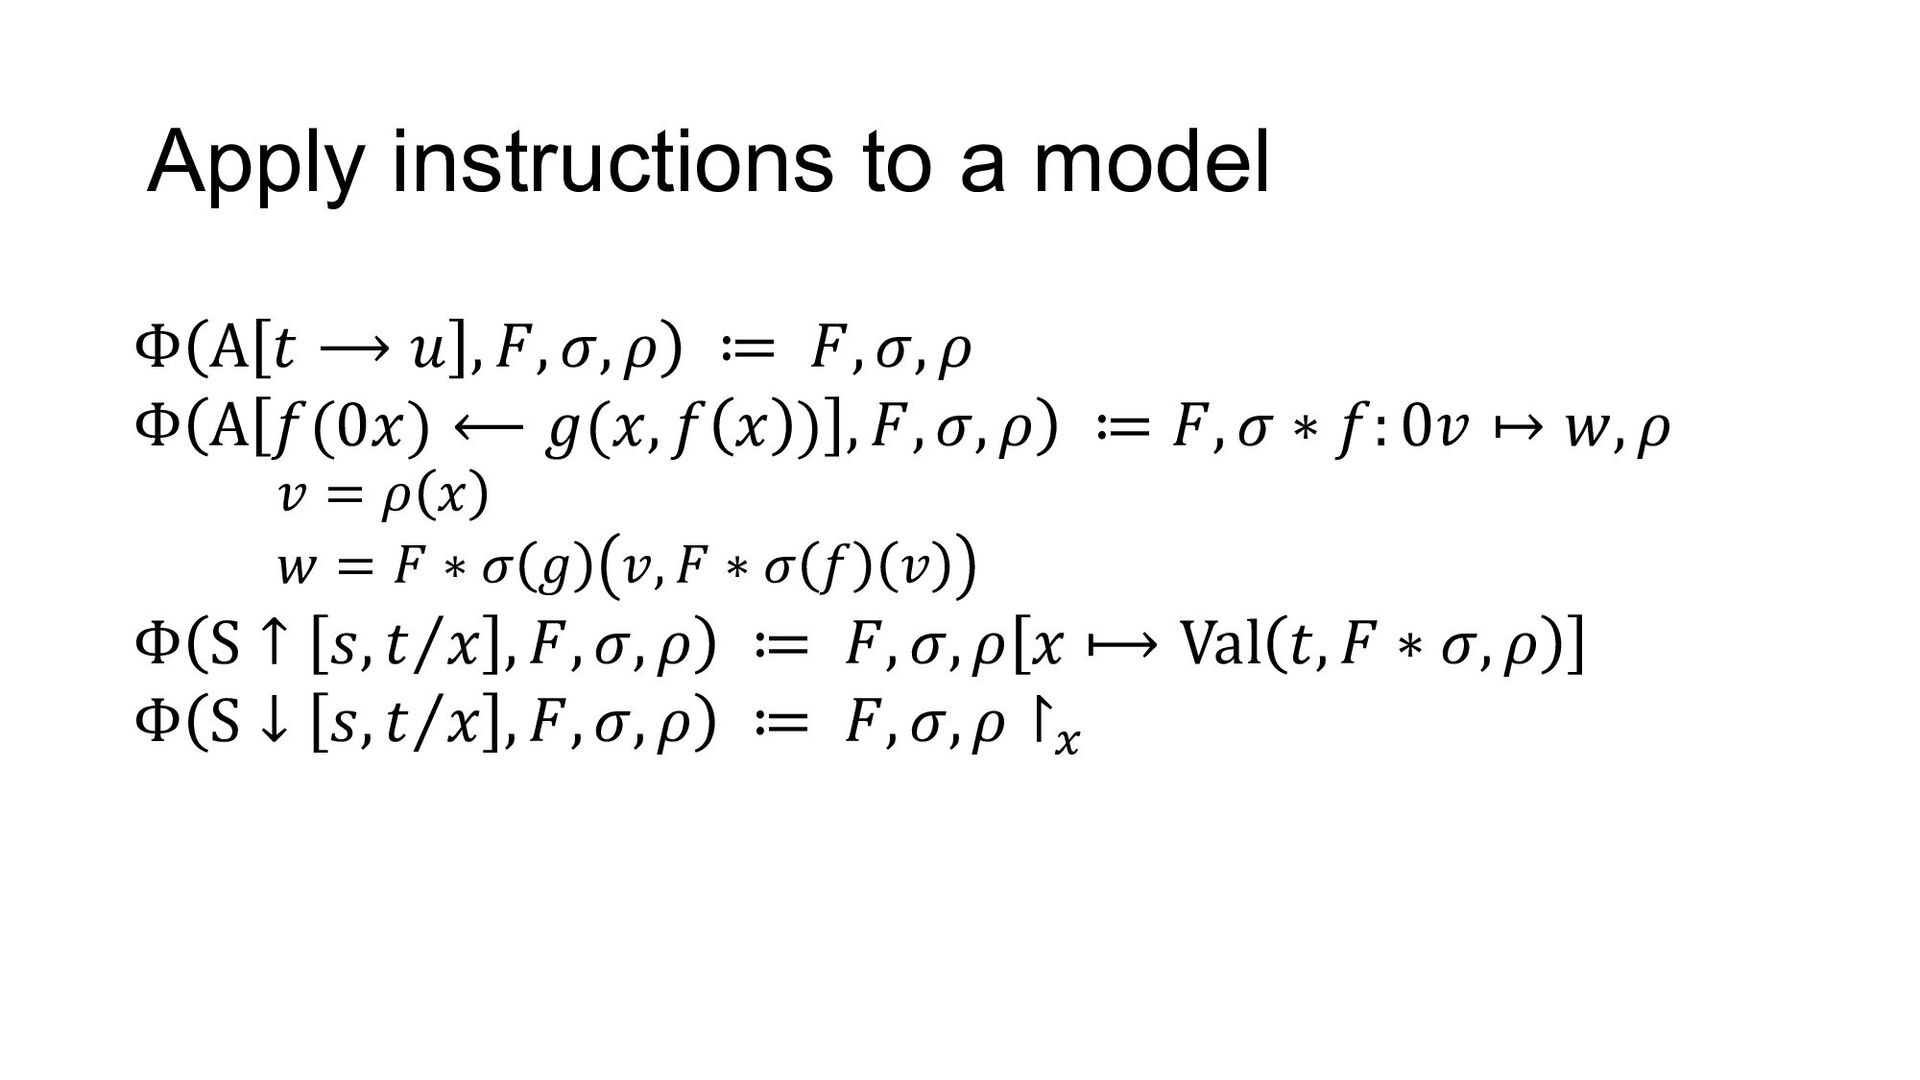
  38. Apply instructions to a model Φ A 𝑡 ⟶ 𝑢

    , 𝐹, 𝜎, 𝜌 ≔ 𝐹, 𝜎, 𝜌 Φ A 𝑓(0𝑥) ⟵ 𝑔(𝑥, 𝑓 𝑥 ) , 𝐹, 𝜎, 𝜌 ≔ 𝐹, 𝜎 ∗ 𝑓: 0𝑣 ↦ 𝑤, 𝜌 𝑣 = 𝜌 𝑥 𝑤 = 𝐹 ∗ 𝜎 𝑔 𝑣, 𝐹 ∗ 𝜎 𝑓 𝑣 Φ S ↑ 𝑠, ⁄ 𝑡 𝑥 , 𝐹, 𝜎, 𝜌 ≔ 𝐹, 𝜎, 𝜌 𝑥 ⟼ Val 𝑡, 𝐹 ∗ 𝜎, 𝜌 Φ S ↓ 𝑠, ⁄ 𝑡 𝑥 , 𝐹, 𝜎, 𝜌 ≔ 𝐹, 𝜎, 𝜌 ↾+
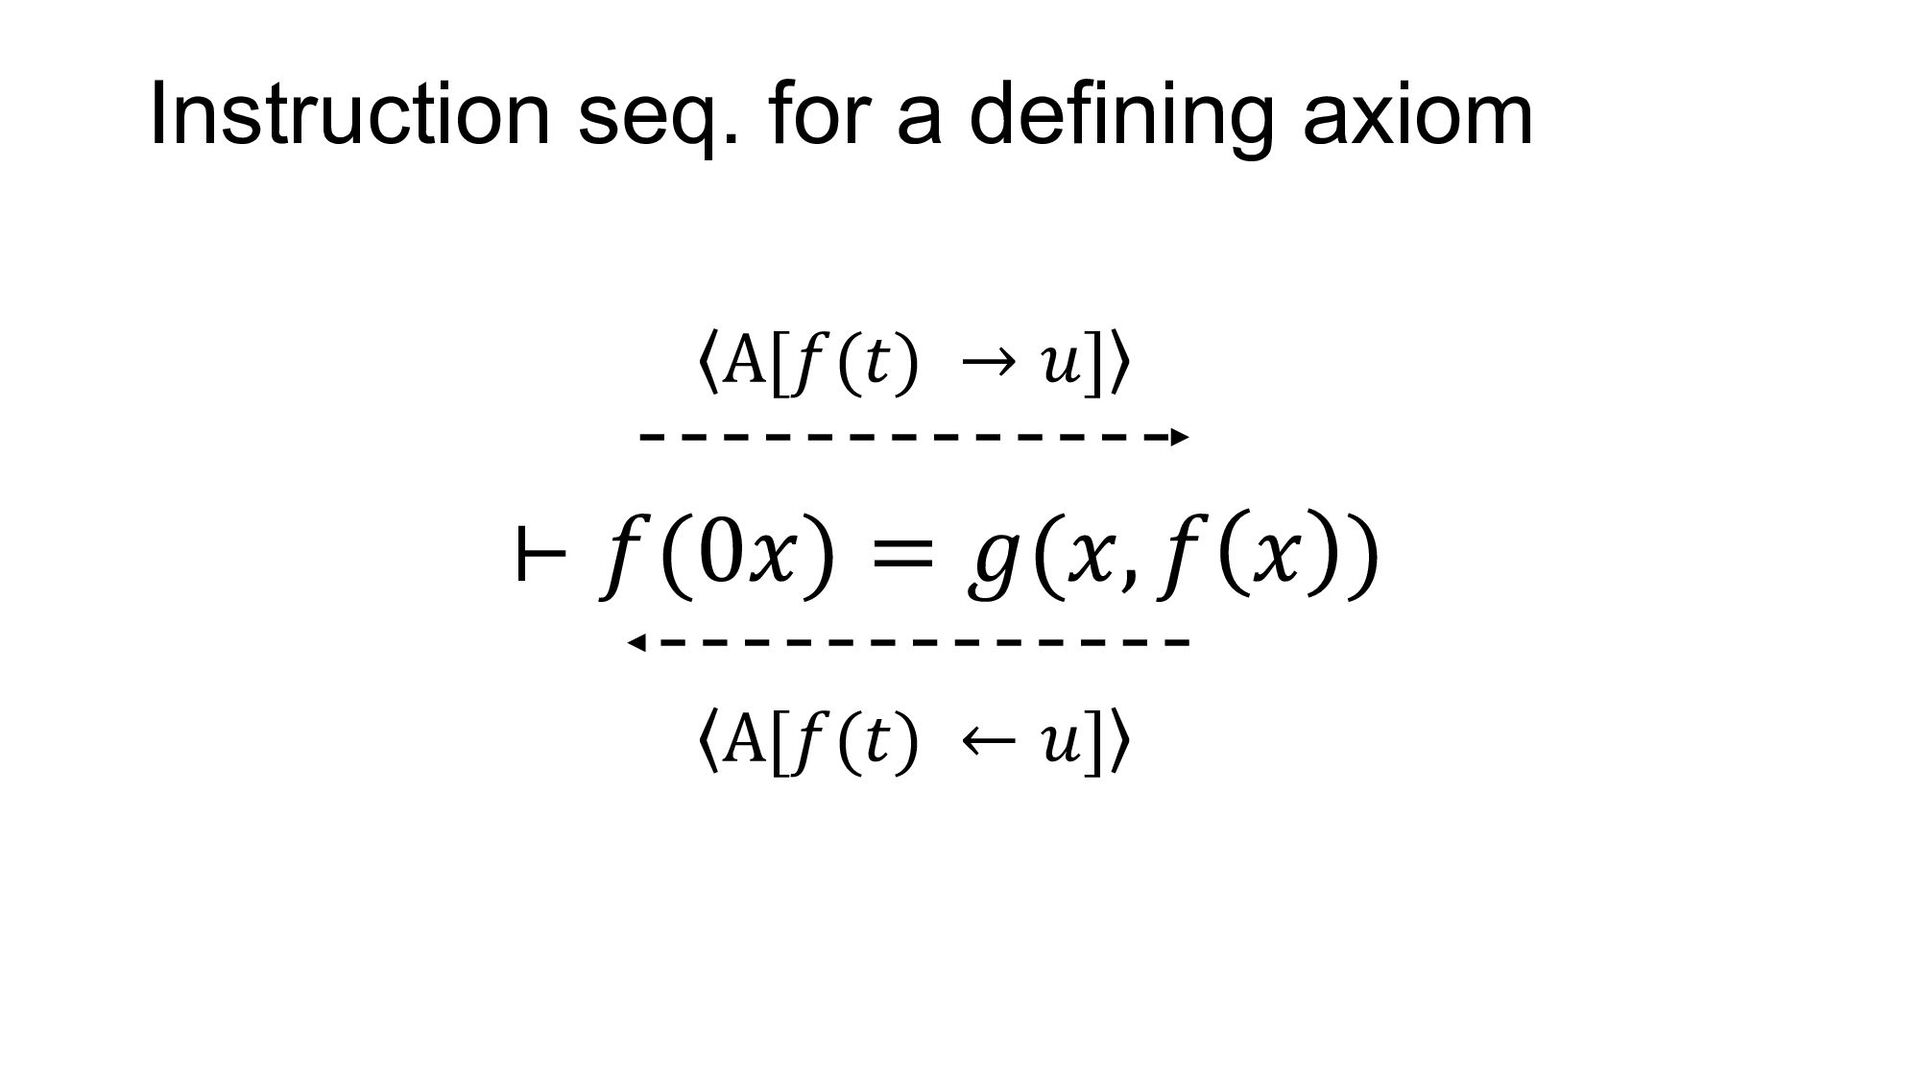
  39. Instruction seq. for a defining axiom ⊢ 𝑓(0𝑥) = 𝑔(𝑥,
    𝑓 𝑥 ) A[𝑓(𝑡) → 𝑢] A[𝑓(𝑡) ← 𝑢]
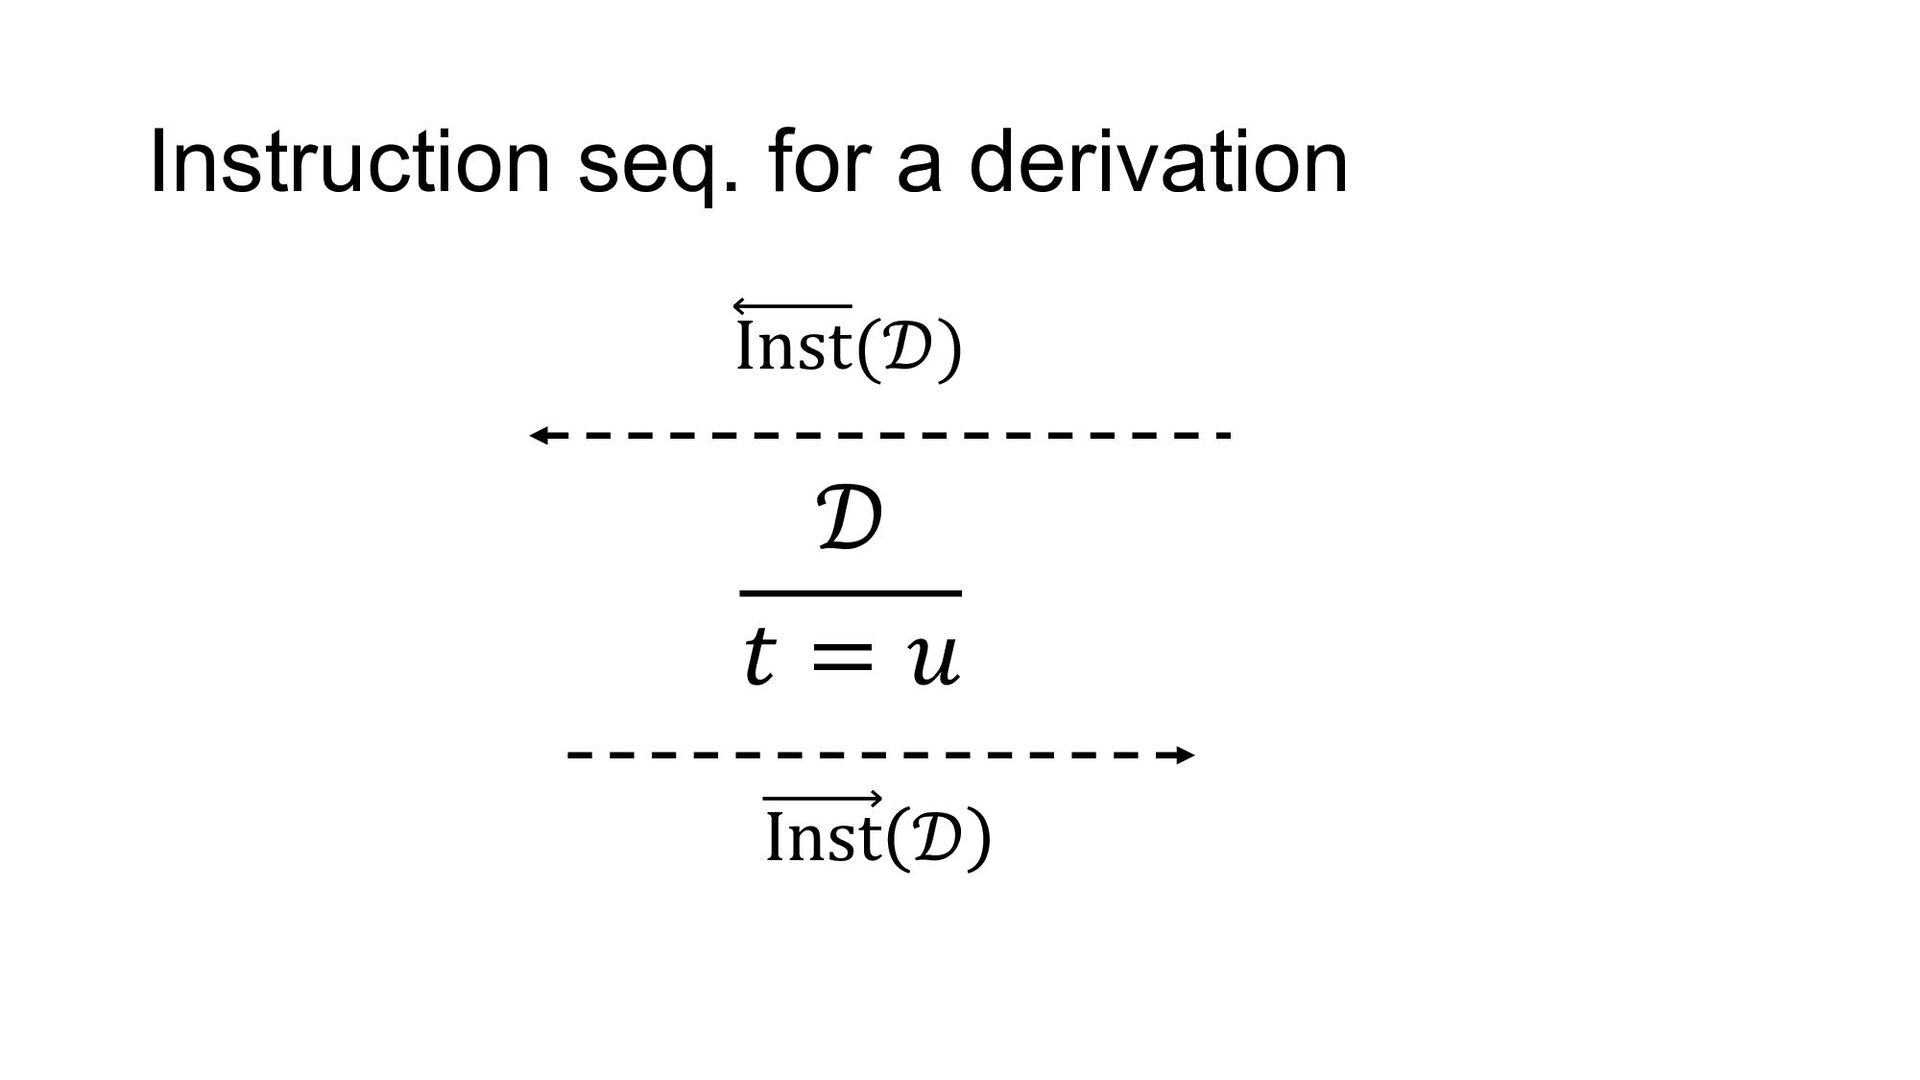
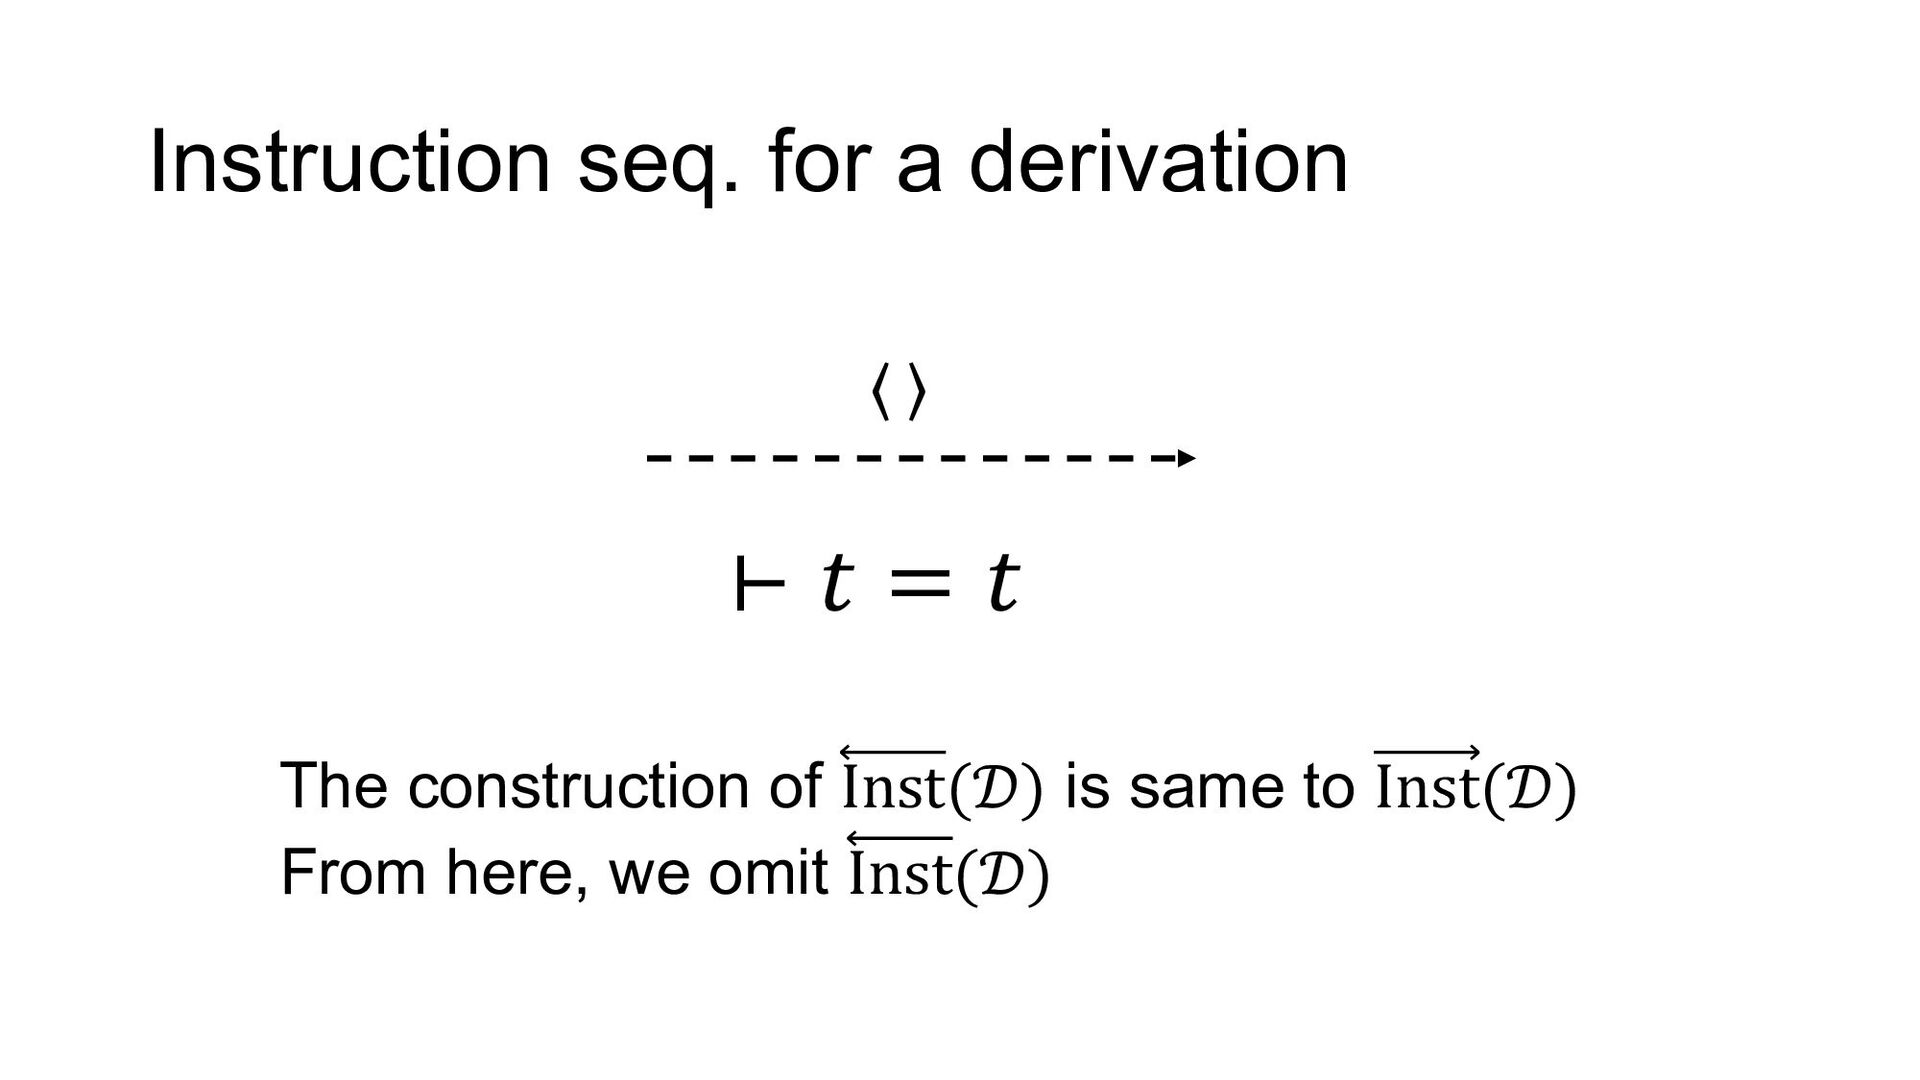
  40. ⊢ 𝑡 = 𝑡 The construction of Inst(𝒟) is same

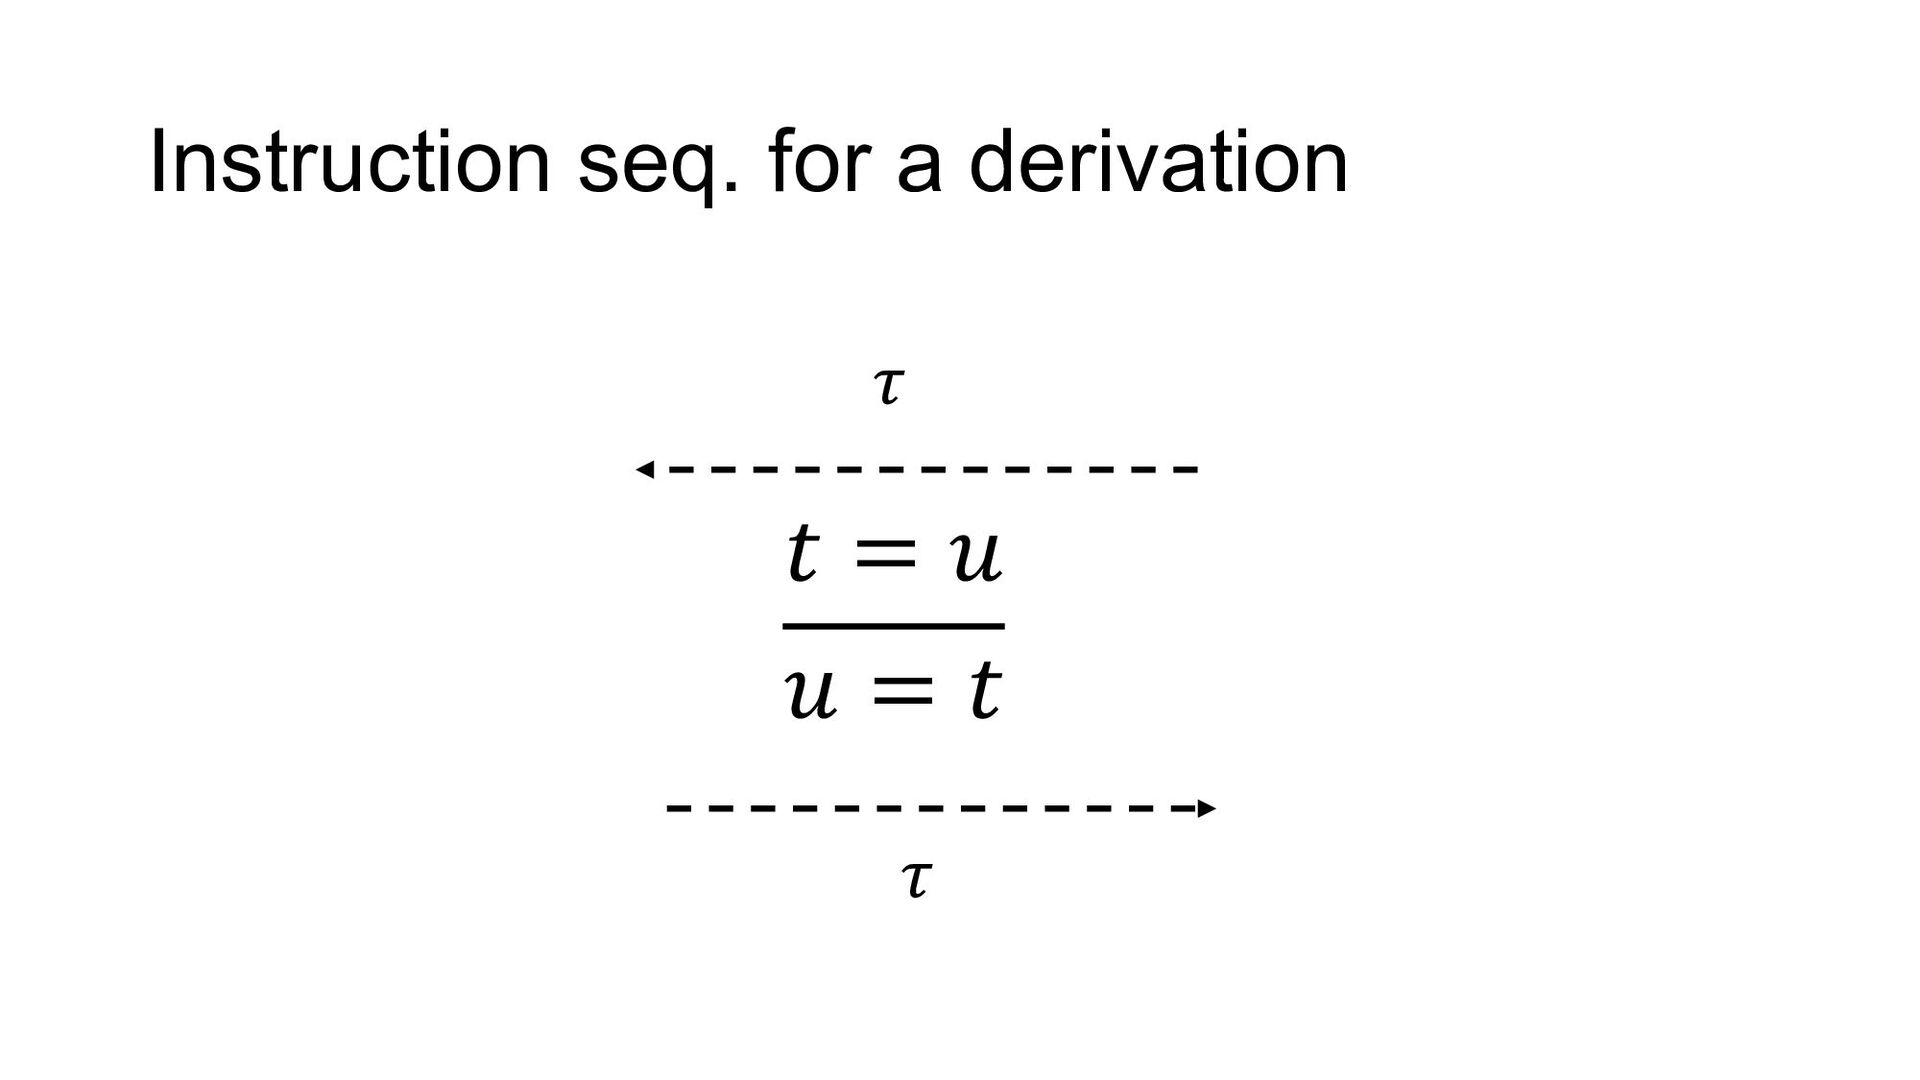
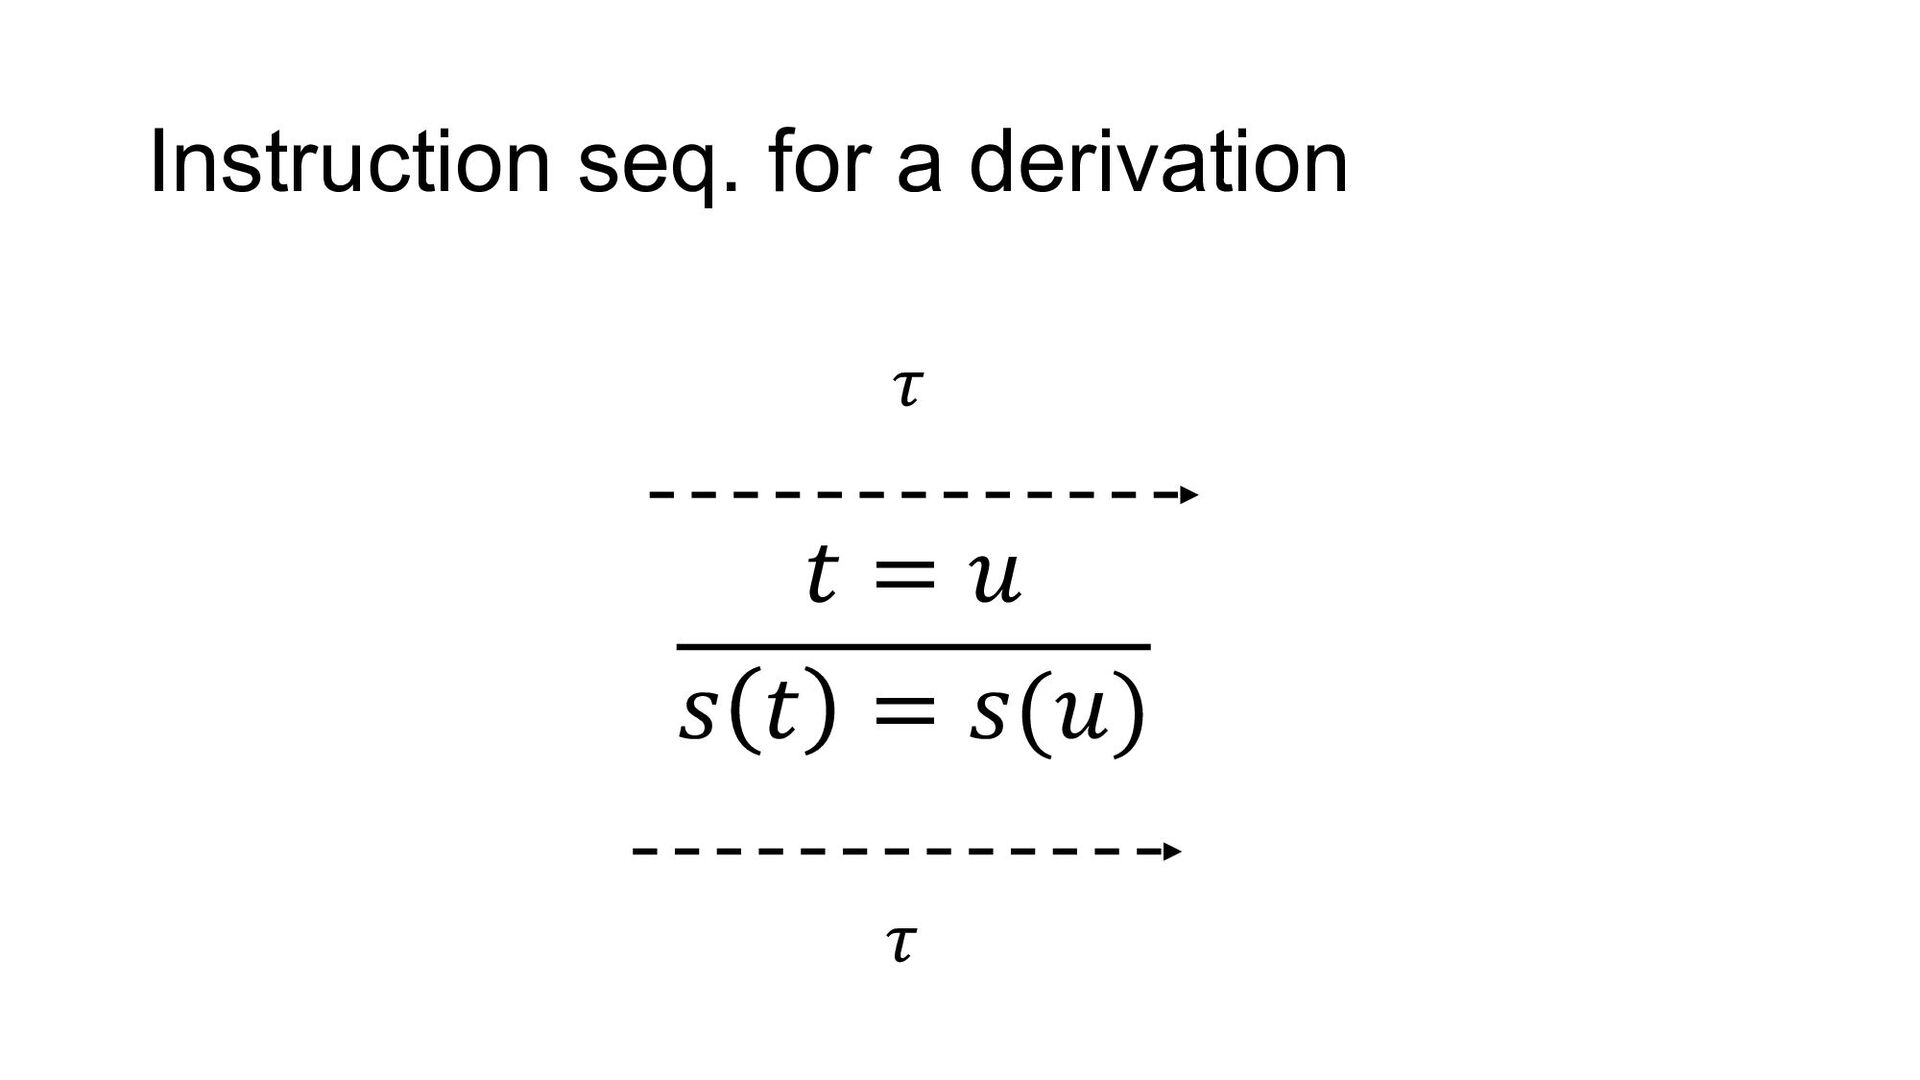
    to Inst(𝒟) From here, we omit Inst(𝒟) Instruction seq. for a derivation
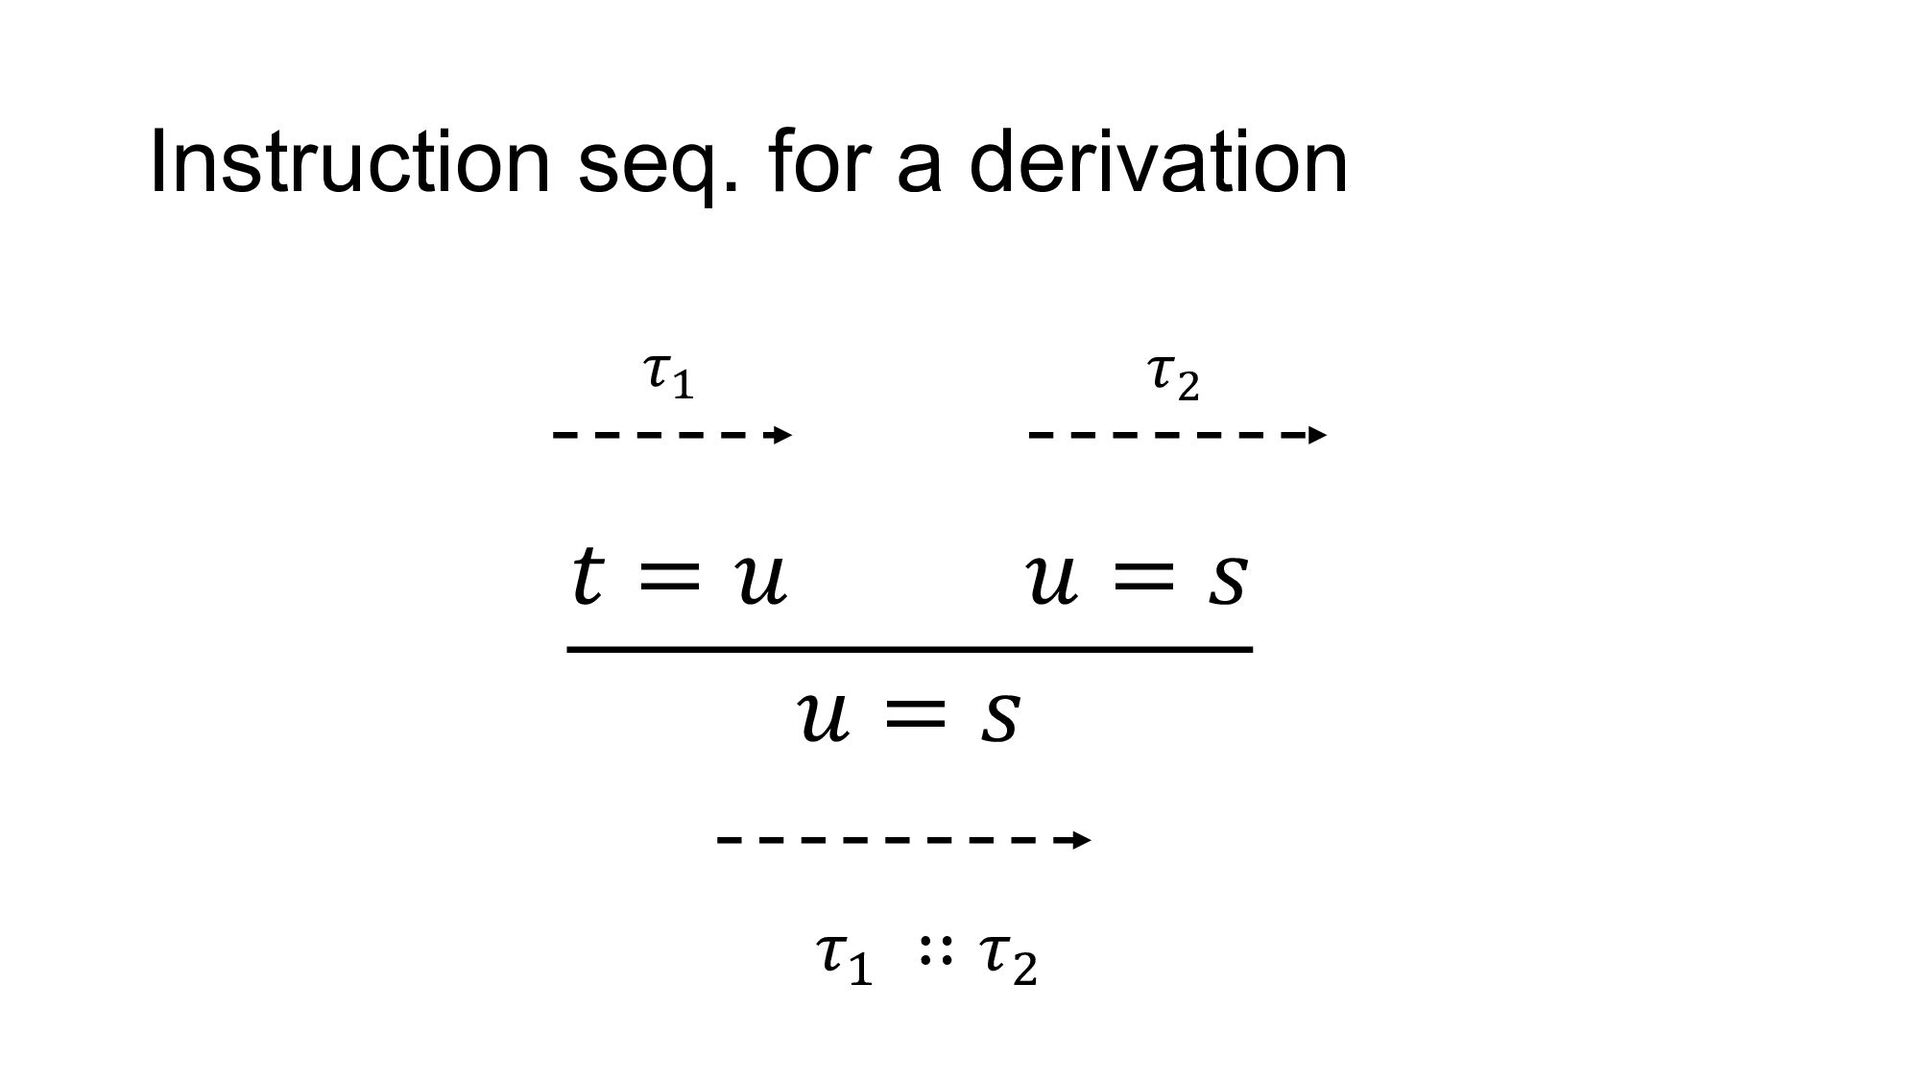
  41. 𝑡 = 𝑢 𝑢 = 𝑠 𝑢 = 𝑠 𝜏#

    𝜏" 𝜏! ∷ 𝜏" Instruction seq. for a derivation
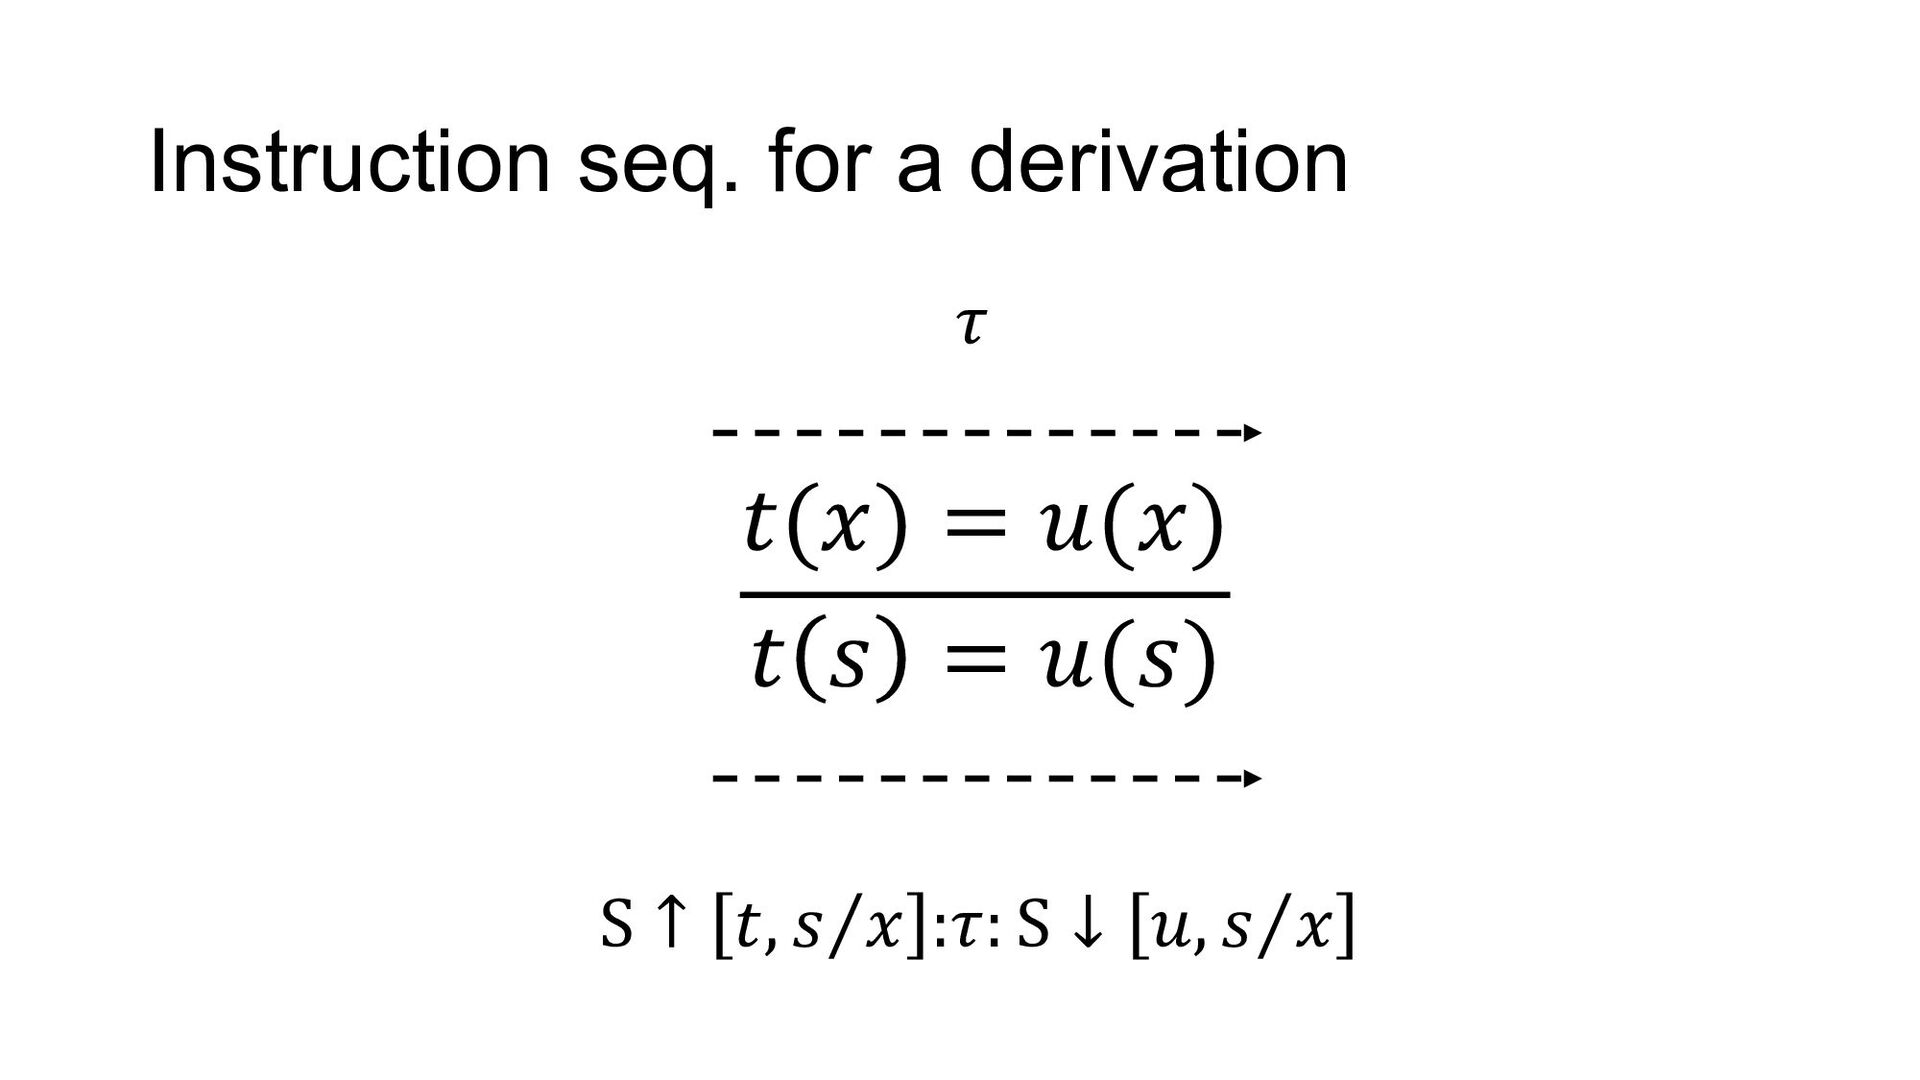
  42. 𝑡(𝑥) = 𝑢(𝑥) 𝑡 𝑠 = 𝑢(𝑠) 𝜏 S ↑

    𝑡, ⁄ 𝑠 𝑥 :𝜏: S ↓ 𝑢, ⁄ 𝑠 𝑥 Instruction seq. for a derivation
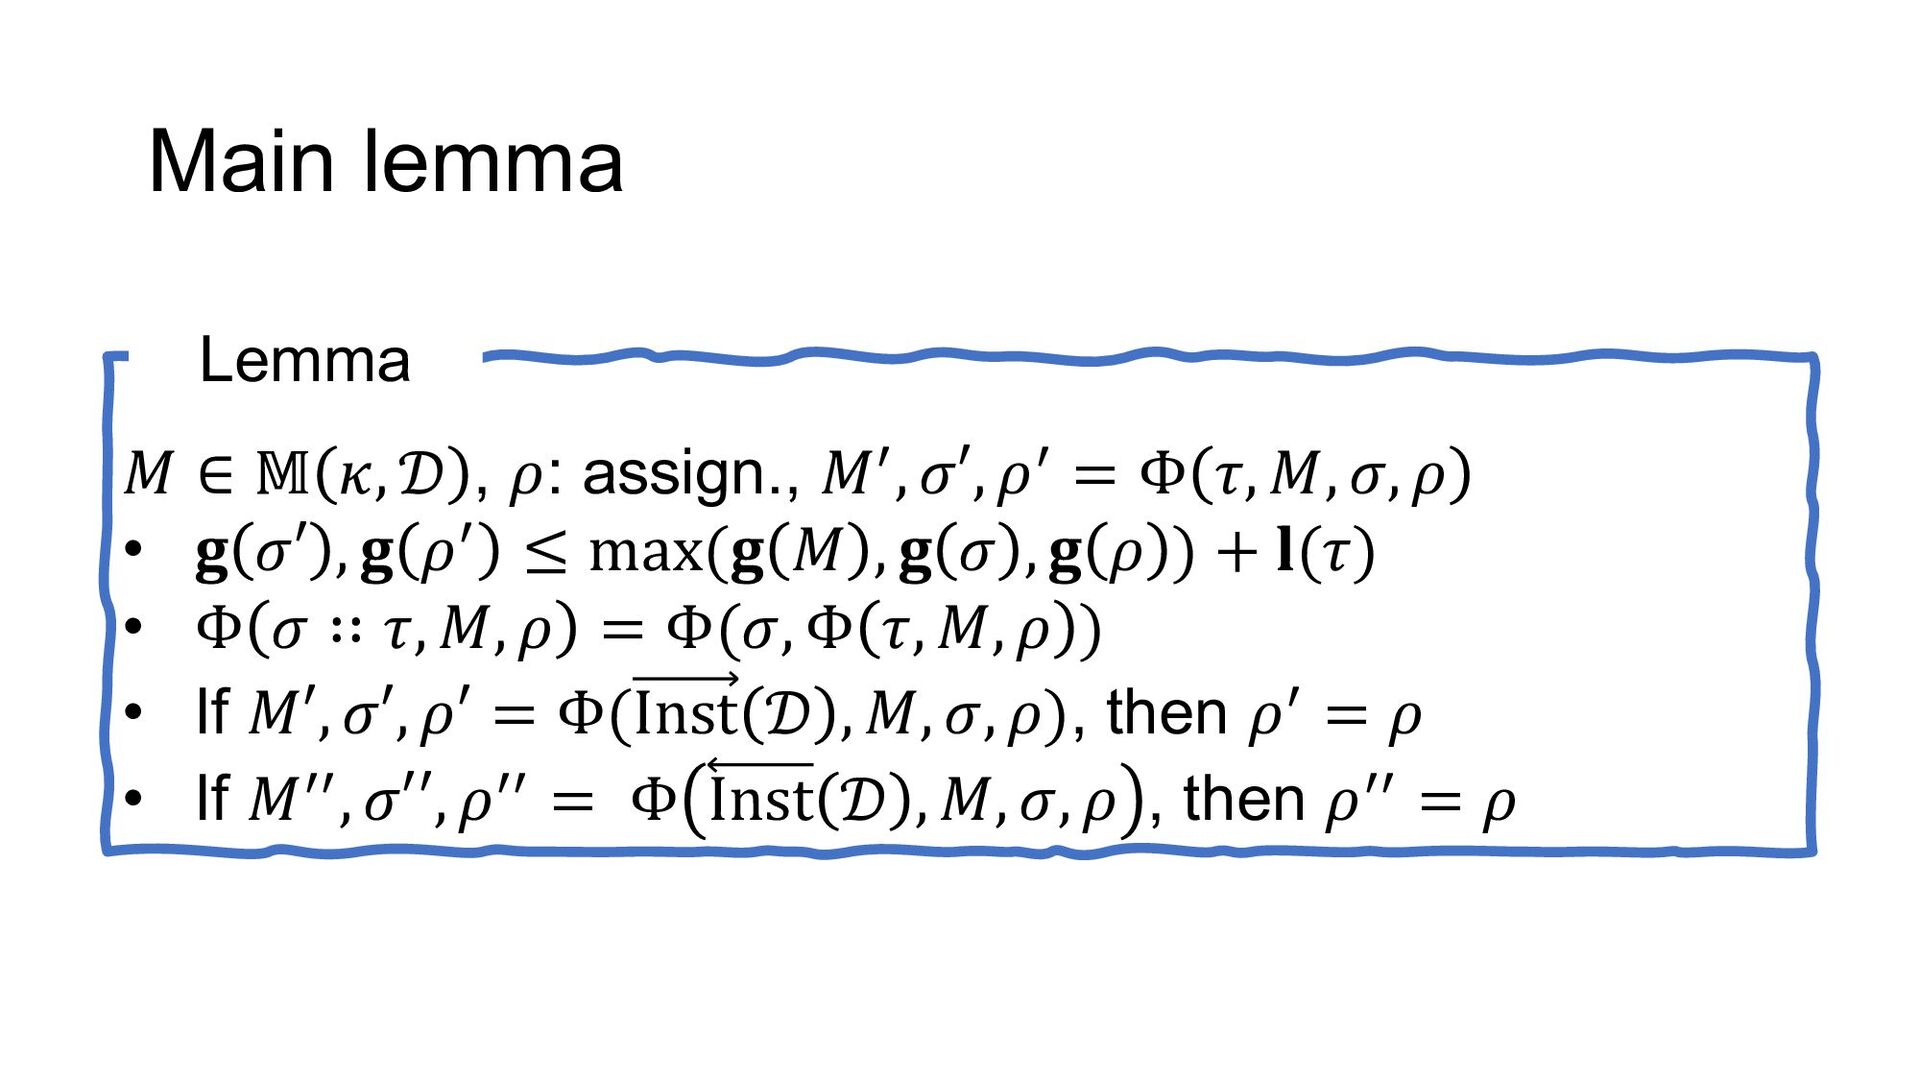
  43. Main lemma 𝑀 ∈ 𝕄 𝜅, 𝒟 , 𝜌: assign.,

    𝑀(, 𝜎′, 𝜌( = Φ 𝜏, 𝑀, 𝜎, 𝜌 • 𝐠 𝜎′ , 𝐠 𝜌( ≤ max(𝐠 𝑀 , 𝐠 𝜎 , 𝐠 𝜌 ) + 𝐥(𝜏) • Φ 𝜎 ∷ 𝜏, 𝑀, 𝜌 = Φ(𝜎, Φ 𝜏, 𝑀, 𝜌 ) • If 𝑀′, 𝜎′, 𝜌′ = Φ(Inst 𝒟 , 𝑀, 𝜎, 𝜌), then 𝜌( = 𝜌 • If 𝑀((, 𝜎′′, 𝜌(( = Φ Inst 𝒟 , 𝑀, 𝜎, 𝜌 , then 𝜌(( = 𝜌 Lemma
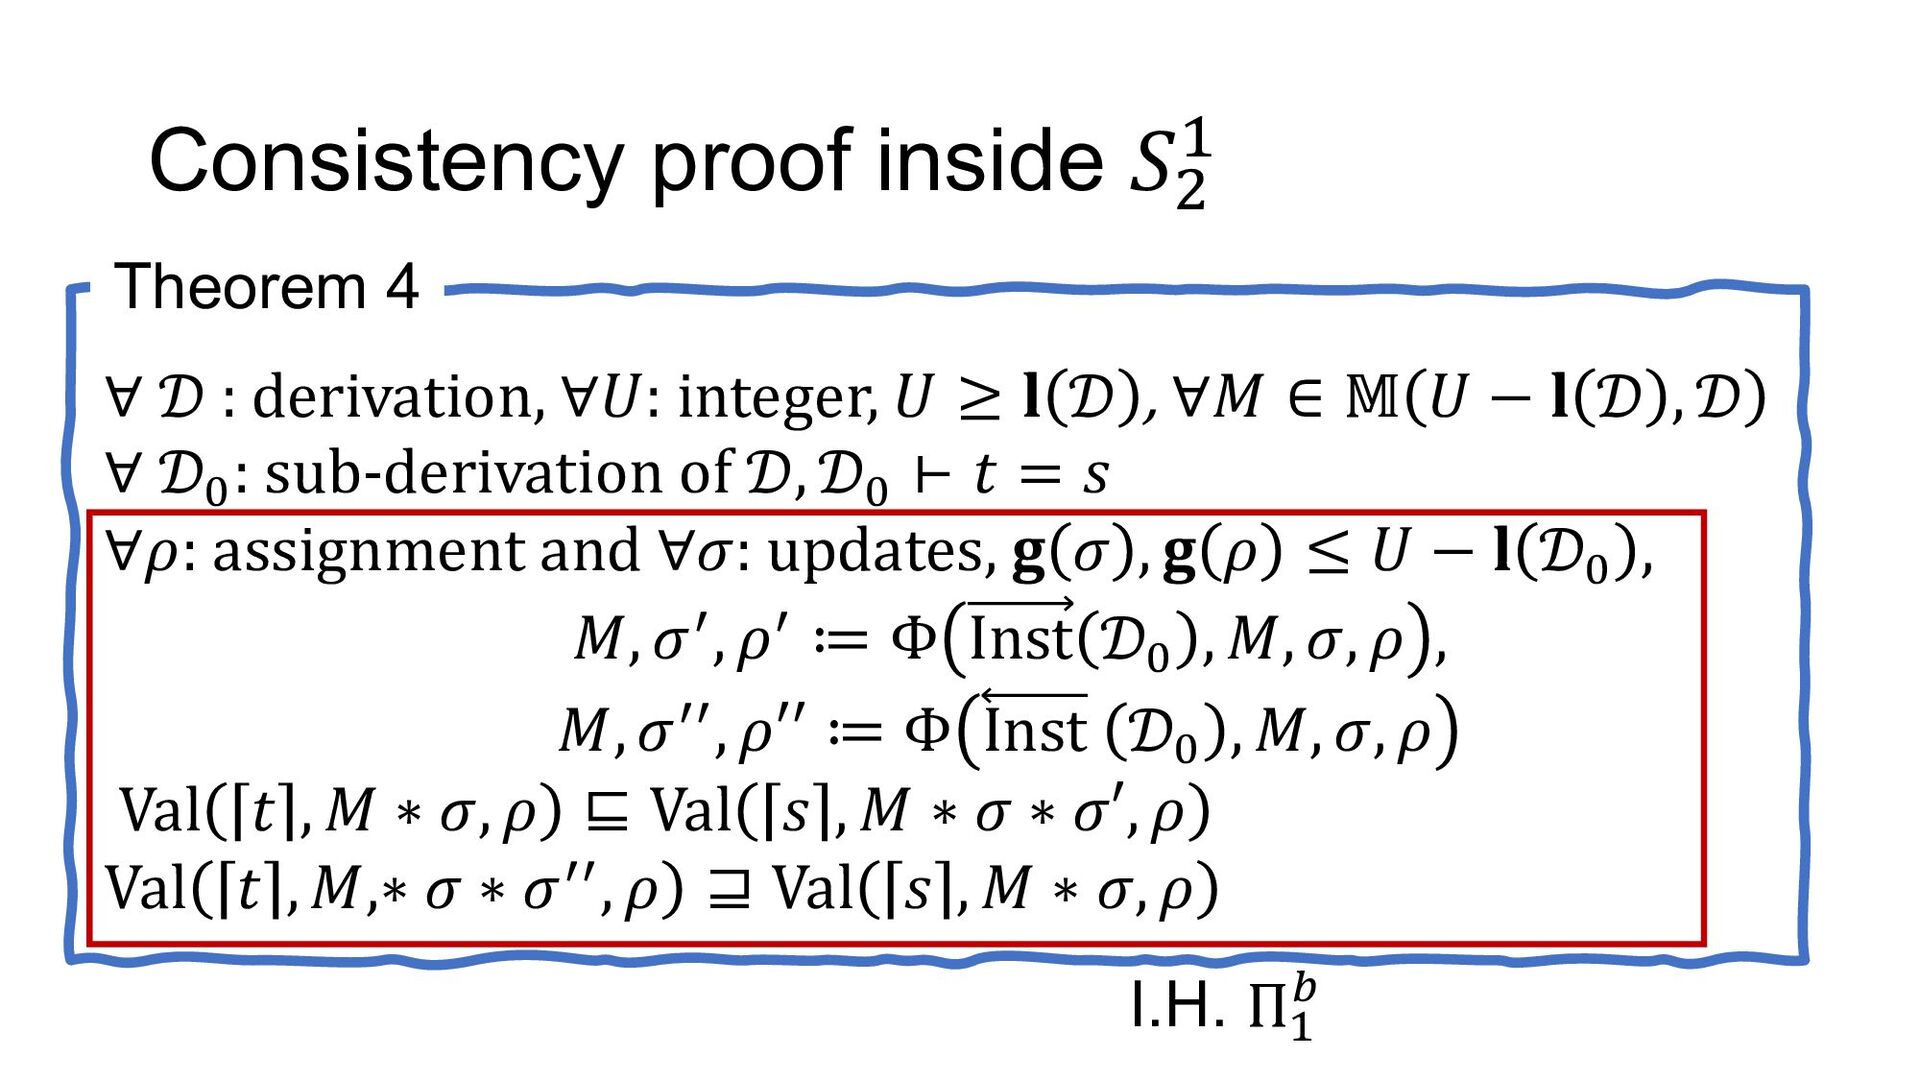
  44. Consistency proof inside 𝑆2 ` Theorem 4 ∀ 𝒟 :

    derivation, ∀𝑈: integer, 𝑈 ≥ 𝐥 𝒟 , ∀𝑀 ∈ 𝕄 𝑈 − 𝐥 𝒟 , 𝒟 ∀ 𝒟* : sub-derivation of 𝒟, 𝒟* ⊢ 𝑡 = 𝑠 ∀𝜌: assignment and ∀𝜎: updates, 𝐠 𝜎 , 𝐠 𝜌 ≤ 𝑈 − 𝐥 𝒟* , 𝑀, 𝜎(, 𝜌( ≔ Φ Inst 𝒟* , 𝑀, 𝜎, 𝜌 , 𝑀, 𝜎((, 𝜌′′ ≔ Φ Inst 𝒟* , 𝑀, 𝜎, 𝜌 Val 𝑡 , 𝑀 ∗ 𝜎, 𝜌 ⊑ Val 𝑠 , 𝑀 ∗ 𝜎 ∗ 𝜎′, 𝜌 Val 𝑡 , 𝑀,∗ 𝜎 ∗ 𝜎((, 𝜌 ⊒ Val 𝑠 , 𝑀 ∗ 𝜎, 𝜌 I.H. Π# %

More Decks by Yoriyuki Yamagata

Other Decks in Research