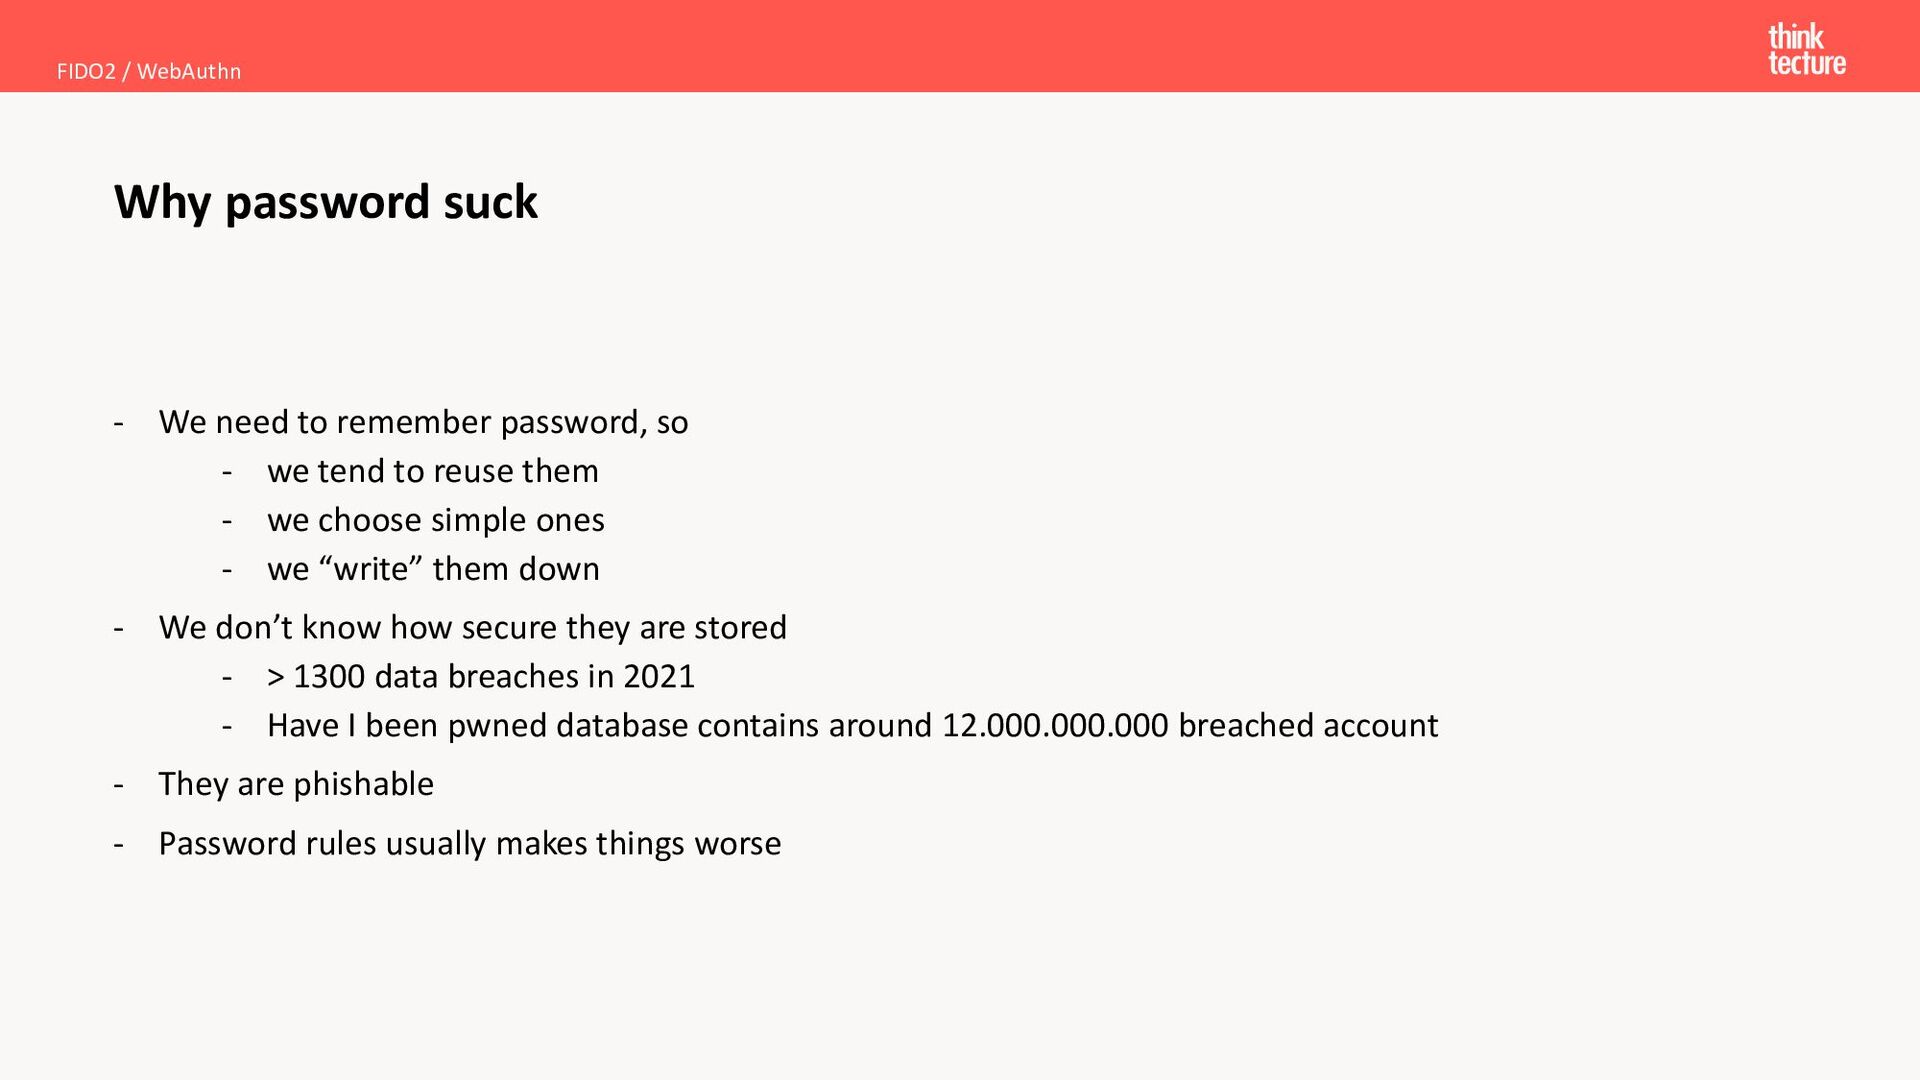
to reuse them - we choose simple ones - we “write” them down - We don’t know how secure they are stored - > 1300 data breaches in 2021 - Have I been pwned database contains around 12.000.000.000 breached account - They are phishable - Password rules usually makes things worse Why password suck FIDO2 / WebAuthn
Cell phone traffic can be easily intercepted - we don’t know how secure they are generated Authenticator Apps - Heavily depends on the phone and app security And both are still phishable and “brute forceable”… But we have MFA with… FIDO2 / WebAuthn
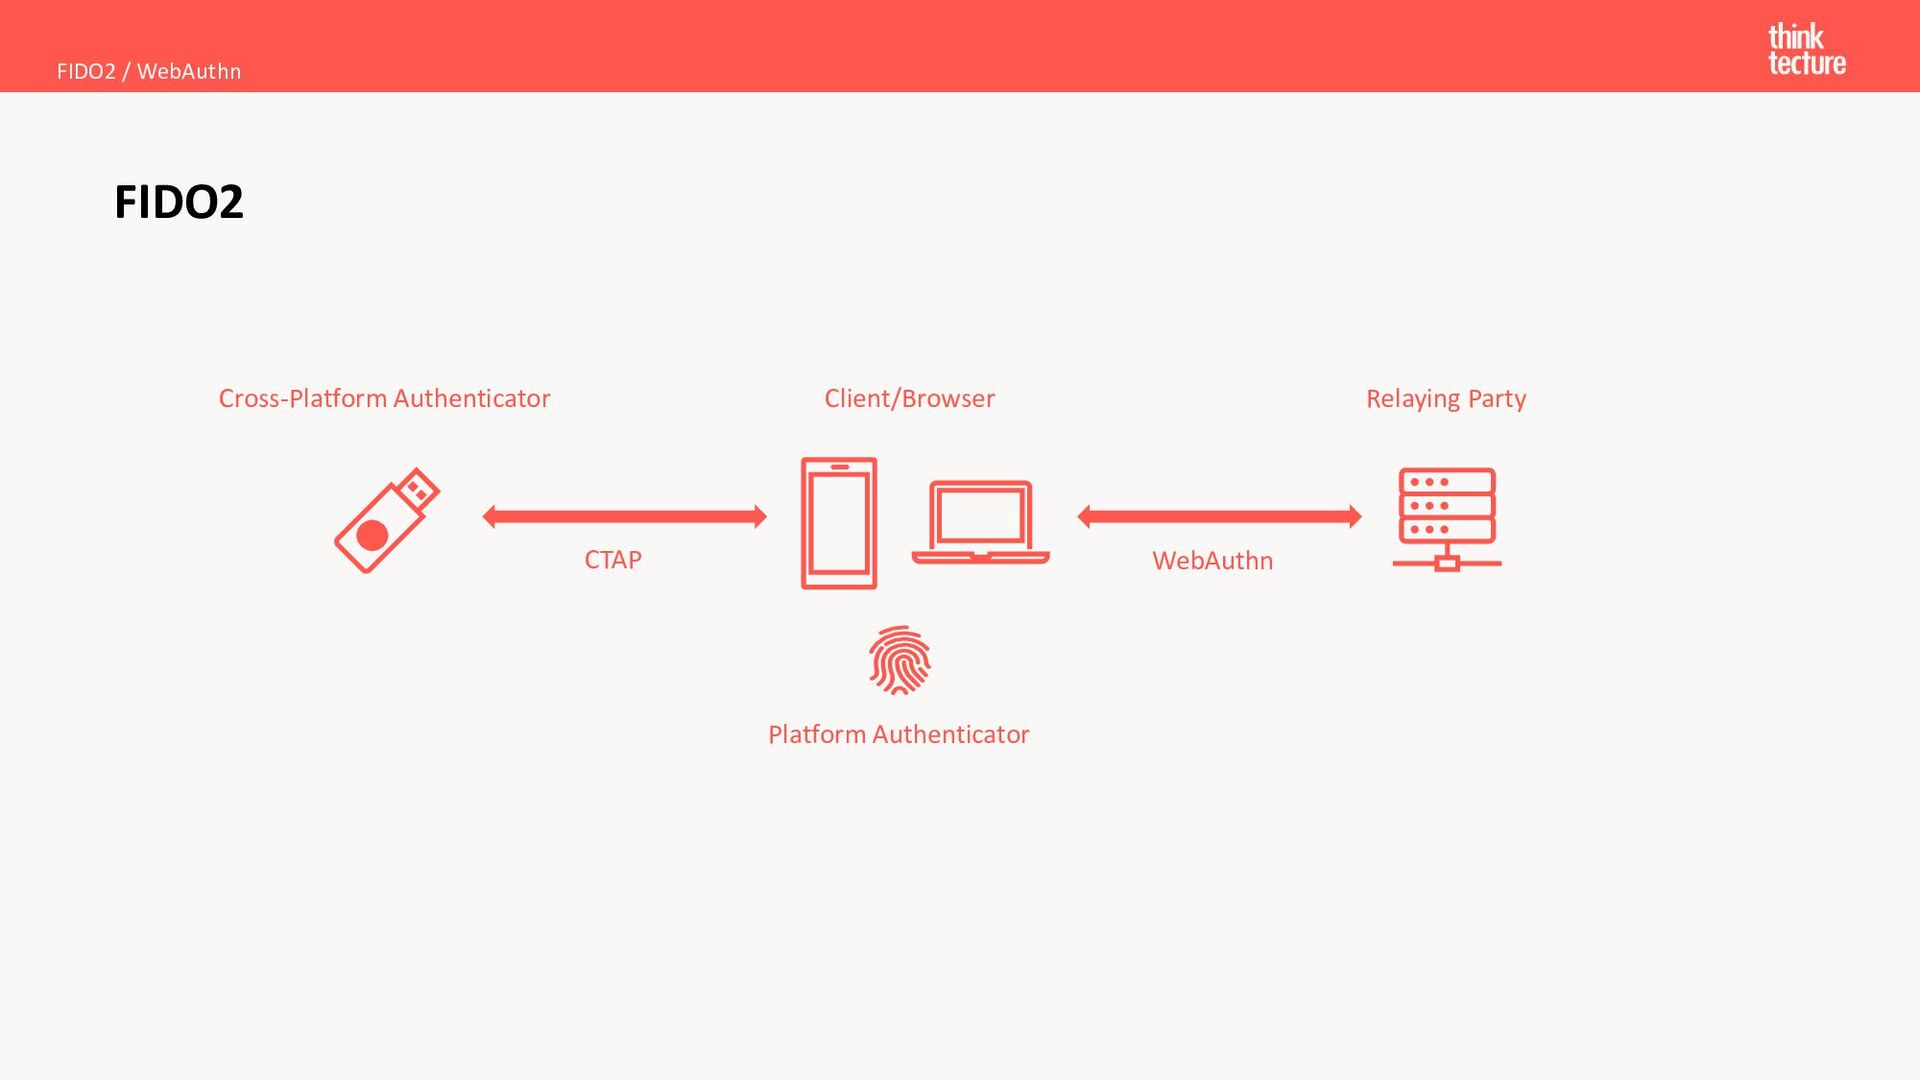
FIDO Alliance and the World Wide Web Consortium (W3C) - CTAP - WebAuthn - The goal is to provide strong authentication without a password - FIDO2 can be used - as an additional factor for authentication - to replace the password (passwordless) - to replace username & password (usernameless / discoverable credentials) - FIDO2 uses Public Key cryptography to ensure strong authentication without passwords - WebAuthn is phishing save FIDO2 FIDO2 / WebAuthn
build into your operating system - Usually needs a TPM - Is bound to your device - Not portable! - User verification depends on operating system and hardware
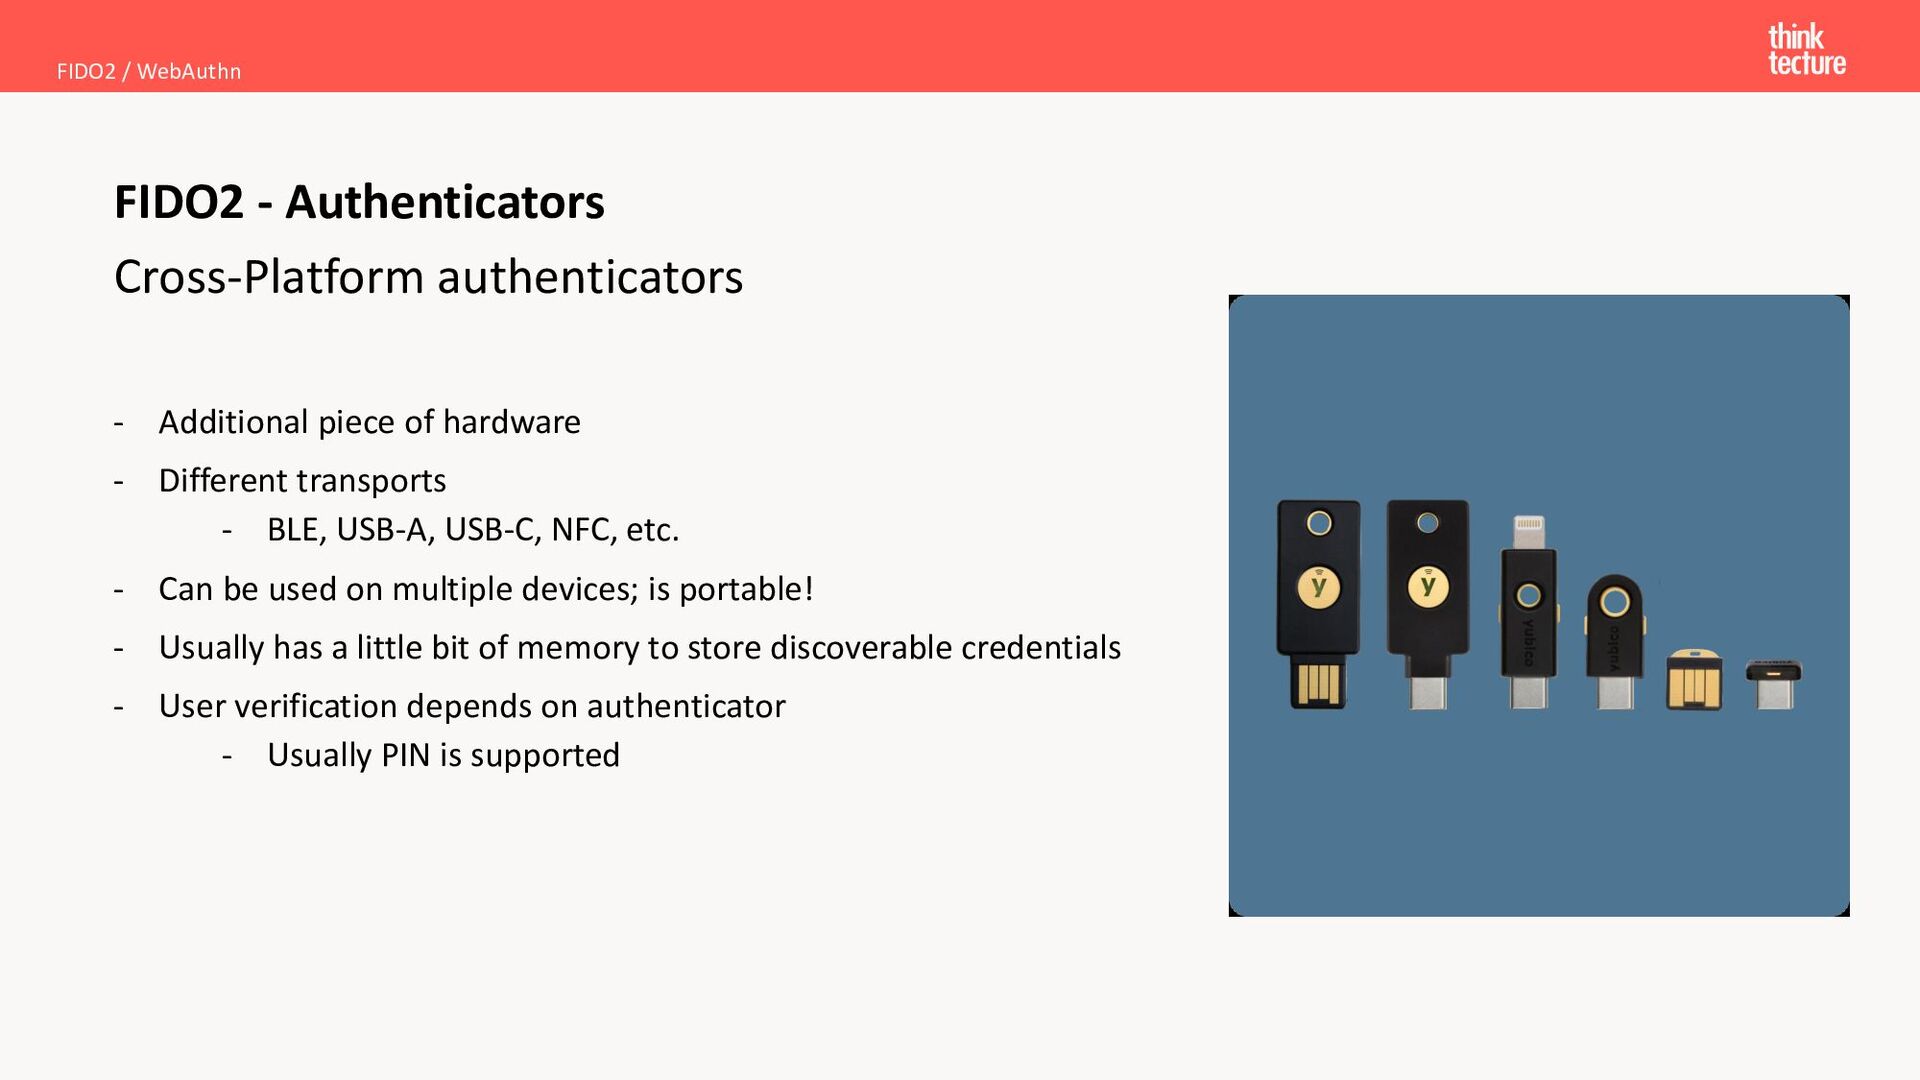
- BLE, USB-A, USB-C, NFC, etc. - Can be used on multiple devices; is portable! - Usually has a little bit of memory to store discoverable credentials - User verification depends on authenticator - Usually PIN is supported FIDO2 / WebAuthn FIDO2 - Authenticators
a challenge (random data) - data describing the RP: display name & id (domain of the RP) - data describing the User: id, name, display name - data about which public keys are acceptable by the RP - data about which authenticator can be used - (cross-)platform authenticator, discoverable credentials, user verification needed - data about which attestation is needed FIDO2 / WebAuthn WebAuthn
authentication) - a public key (needed for later authentication) - ClientDataJson: data created by the client and RP and passed to the authenticator (challenge, origin, etc) - AuthenticatorData: data about the authenticator - attestation data if requested - Format of attestation data varies by authenticator - Metadata Blob provided by FIDO alliance is needed to validate attestation data FIDO2 / WebAuthn WebAuthn
(RP) passes - domain of the RP - a challenge (random data) - one or more credential ids (received via the registration process) - navigator.credentials.get() returns - ClientDataJson: data created by the client and RP and passed to the authenticator (challenge, origin, etc) - AuthenticatorData: data about the authenticator - the signature generated using AuthenticatorData and ClientDataJson by the authenticators private key FIDO2 / WebAuthn WebAuthn
on authenticator device - Authenticators have limited space! - On navigator.credentials.create() set - authenticatorSelection.residentKey: required - authenticatorSelection.requireResidentKey: true - navigator.credentials.get() returns - additionally the user id FIDO2 / WebAuthn WebAuthn
(domain of the RP passed to create() and get()) - Browser created ClientDataJSON and passes it to the authenticator - Contains challange and actual origin - Authenticator signs ClientDataJSON - RP rebuilds ClientDataJSON with its stored data and validates signature - RP id is usually used by the authenticator to derive the private key FIDO2 / WebAuthn WebAuthn
On Windows: everything is passed to Windows Hello - On Linux: Browsers have their own dialogs - Firefox on non windows: Does not work with PIN secured keys - There is no way to “backup” a key. - There is no defined recovery process if key is lost - Fallback to “unsecure” ways like reset via email - If key is lost it must be revocable by the user - Their for it can not be the only way to login - If key is lost and not PIN protected, someone might have free access to your system - Platform-authenticator are currently bound to the machine FIDO2 / WebAuthn WebAuthn
extend WebAuthn - Microsoft, Apple, Google - Synchronization of platform-authenticators is coming - WebAuthn credentials will be tied to your Microsoft-, iCloud-, Google Account - Mobile device will be cross-platform authenticator via BLE in future - Already possible with Chrome and Android - Already usable on a lot of “big” websites - Microsoft Account, Google Account, github, ebay, facebook, etc.. FIDO2 / WebAuthn WebAuthn


 boriswilhelms
 pospome
 yoshidashingo
 ssakita
 sergicalsix
 nobitabashi
 orimanabu
 oidfj
 nagisa53
 nagix
 ayaka_egaaa
 hiccupps
 takuros
 caitiem20
 gurzu
 raygrieselhuber
 reverentgeek
 katiecoart
 dugsong
 coloredviolet
 destraynor
 danielanewman
 aleyda
 cassininazir
 retrage