Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Radius原理与应用培训

Sponsored · SiteGround - Reliable hosting with speed, security, and support you can count on. →
Avatar for codeschool codeschool
September 13, 2013

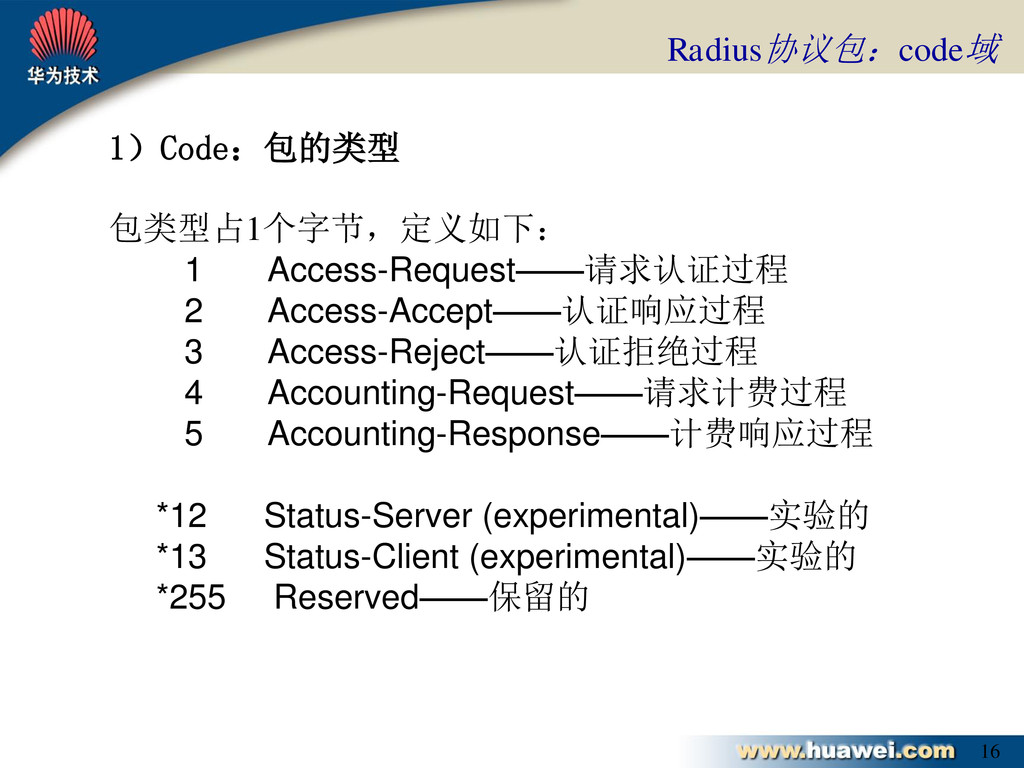
 Radius原理与应用培训

Radius原理与应用培训.pdf

Avatar for codeschool

codeschool

September 13, 2013

More Decks by codeschool

Other Decks in Programming

Transcript

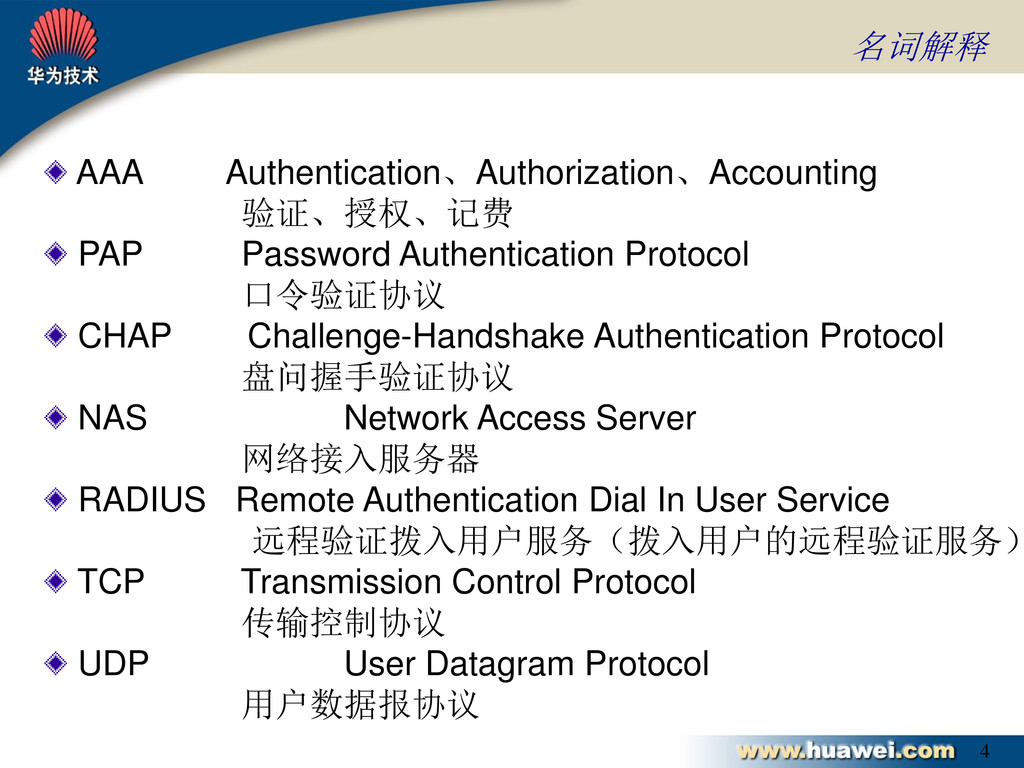
  1. 4 AAA Authentication、Authorization、Accounting 验证、授权、记费 PAP Password Authentication Protocol 口令验证协议 CHAP

    Challenge-Handshake Authentication Protocol 盘问握手验证协议 NAS Network Access Server 网络接入服务器 RADIUS Remote Authentication Dial In User Service 远程验证拨入用户服务(拨入用户的远程验证服务) TCP Transmission Control Protocol 传输控制协议 UDP User Datagram Protocol 用户数据报协议 名词解释
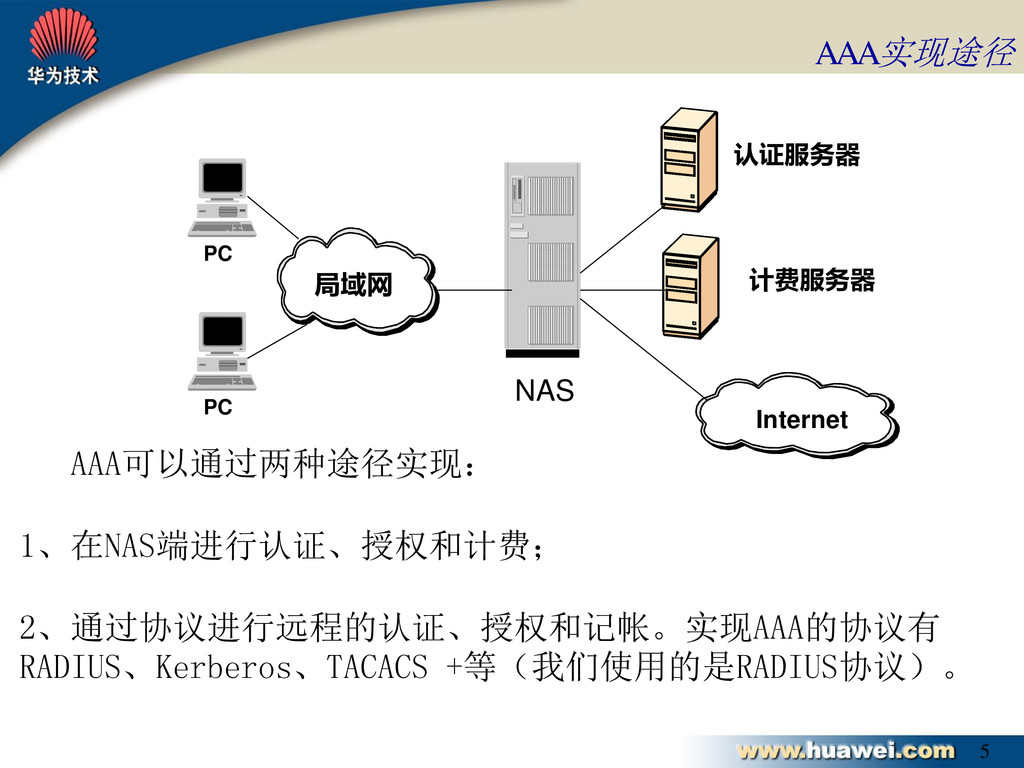
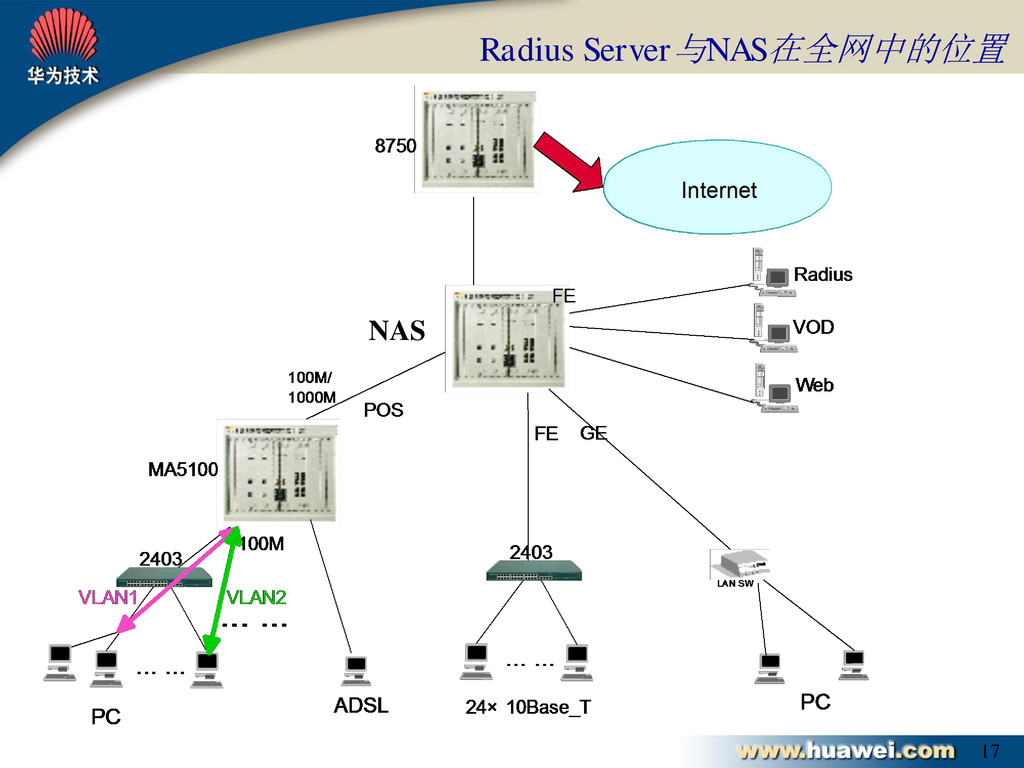
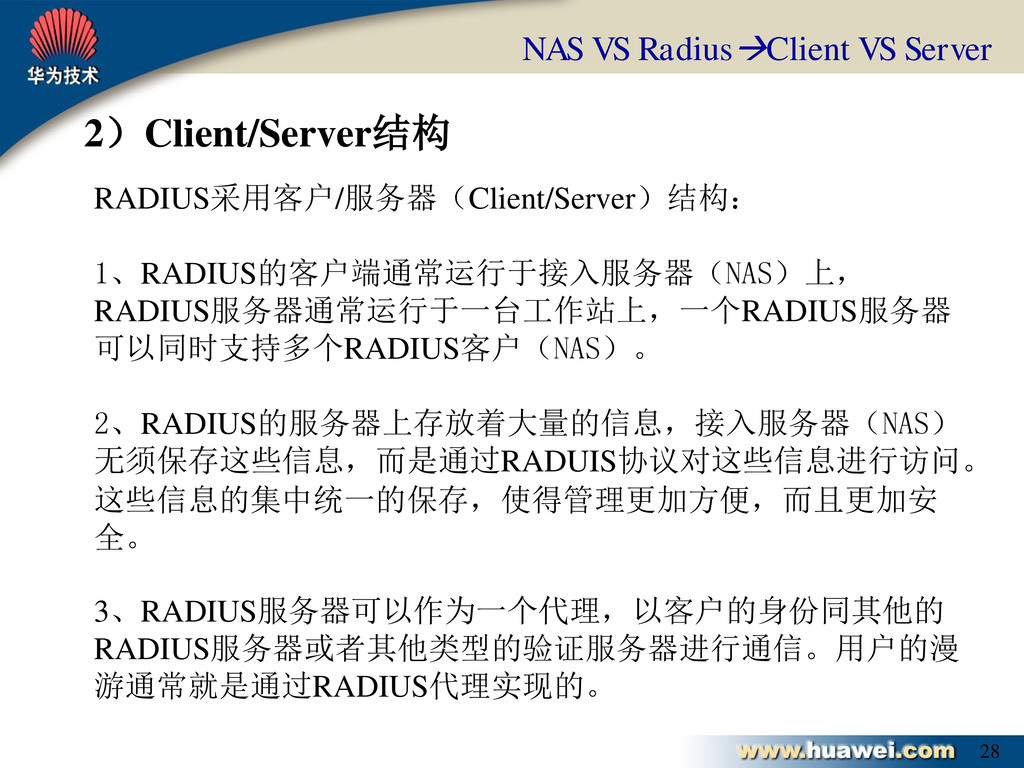
  2. 6 RADIUS 是Remote Authentication Dial In User Service 的简称, MA5200、ISN8850和MD5500上目前使用RADIUS完成对PPP用户

    的认证、授权和计费。 当用户想要通过某个网络(如电话网)与 NAS建立连接从而获 得访问其他网络的权利时,NAS可以选择在NAS上进行本地认证 计费,或把用户信息传递给RADIUS服务器,由Radius进行认证 计费;RADIUS 协议规定了NAS与RADIUS 服务器之间如何传递 用户信息和记账信息;RADIUS服务器负责接收用户的连接请求, 完成验证,并把传递服务给用户所需的配置信息返回给NAS。 AAA实现途径
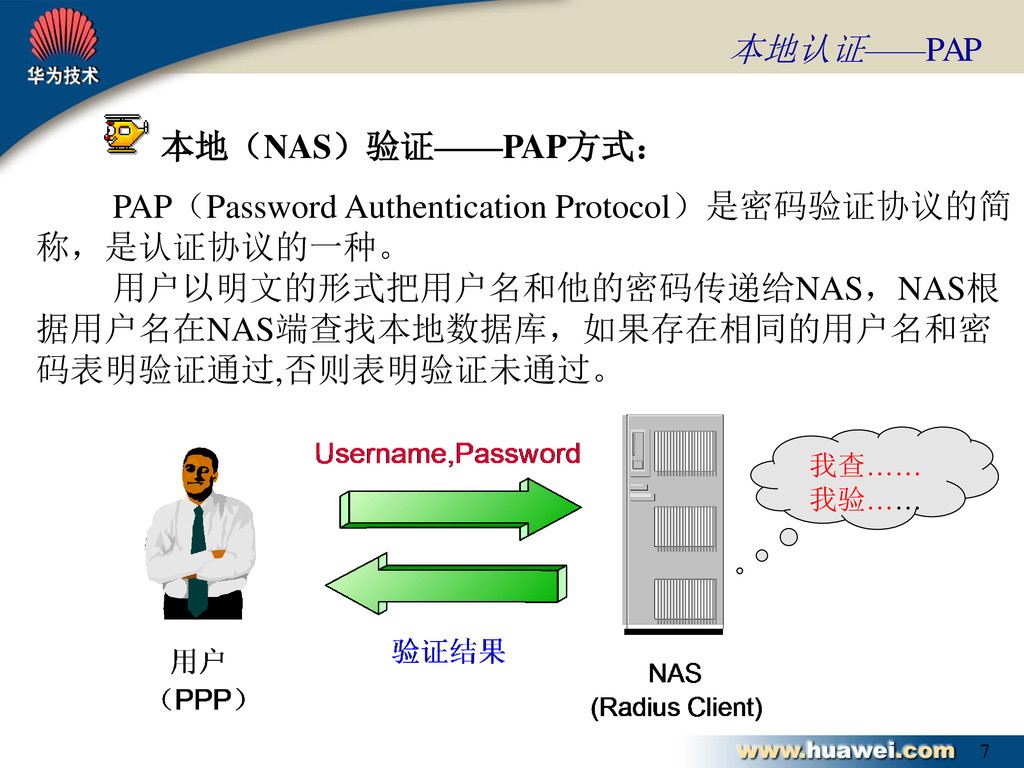
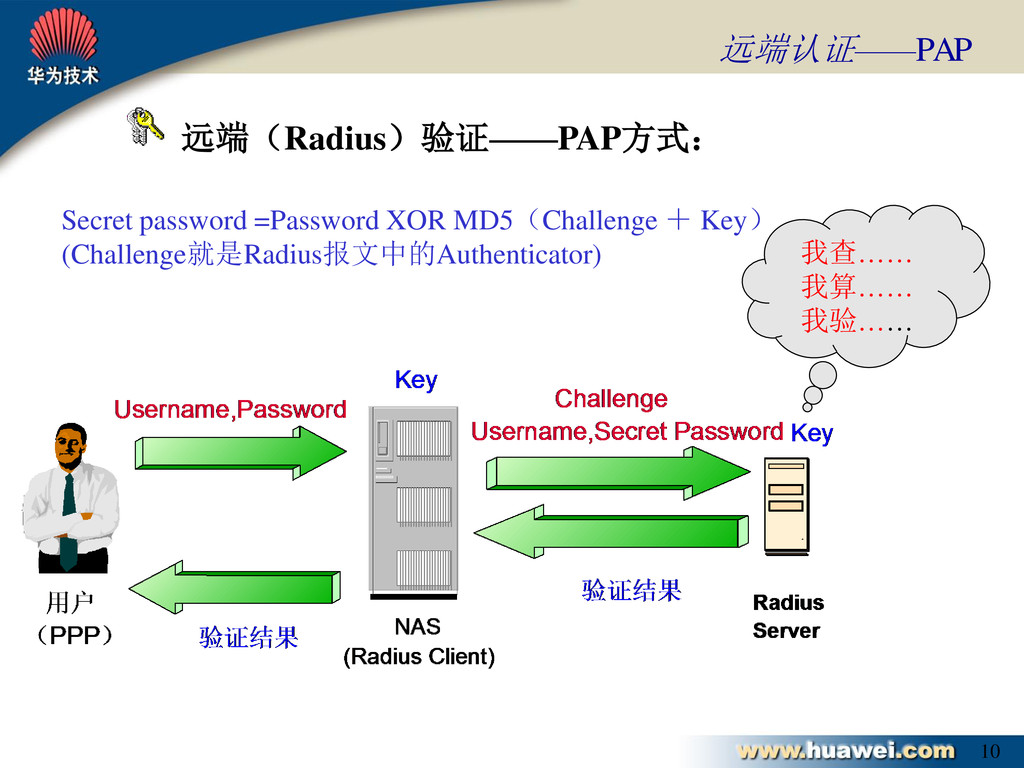
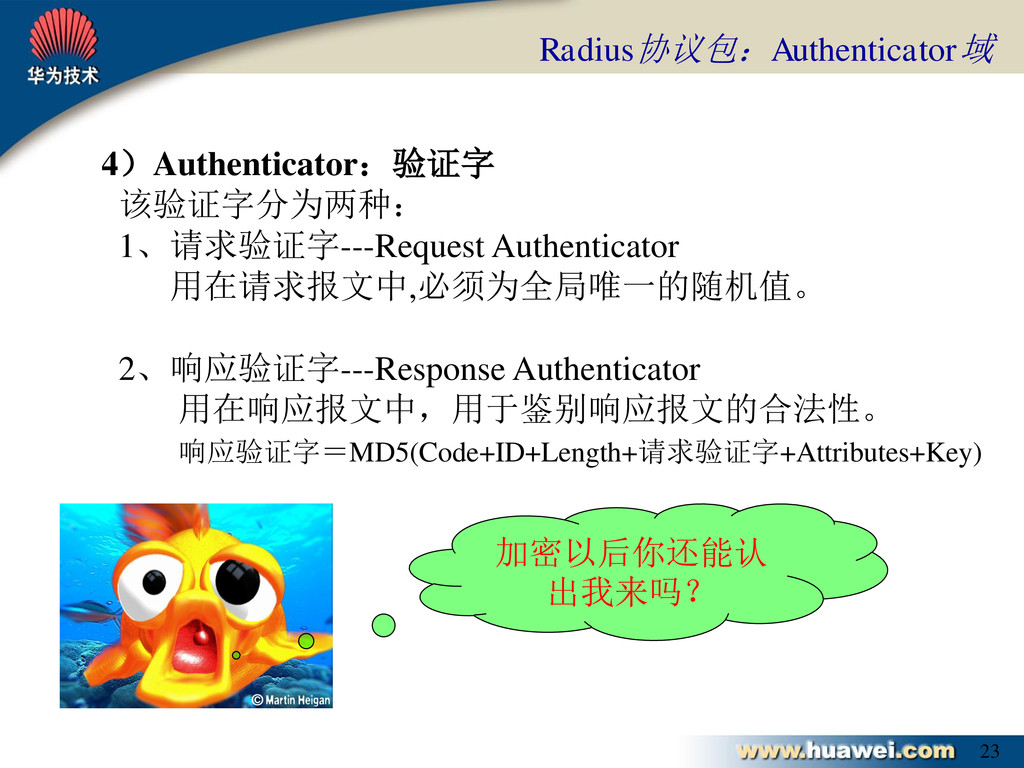
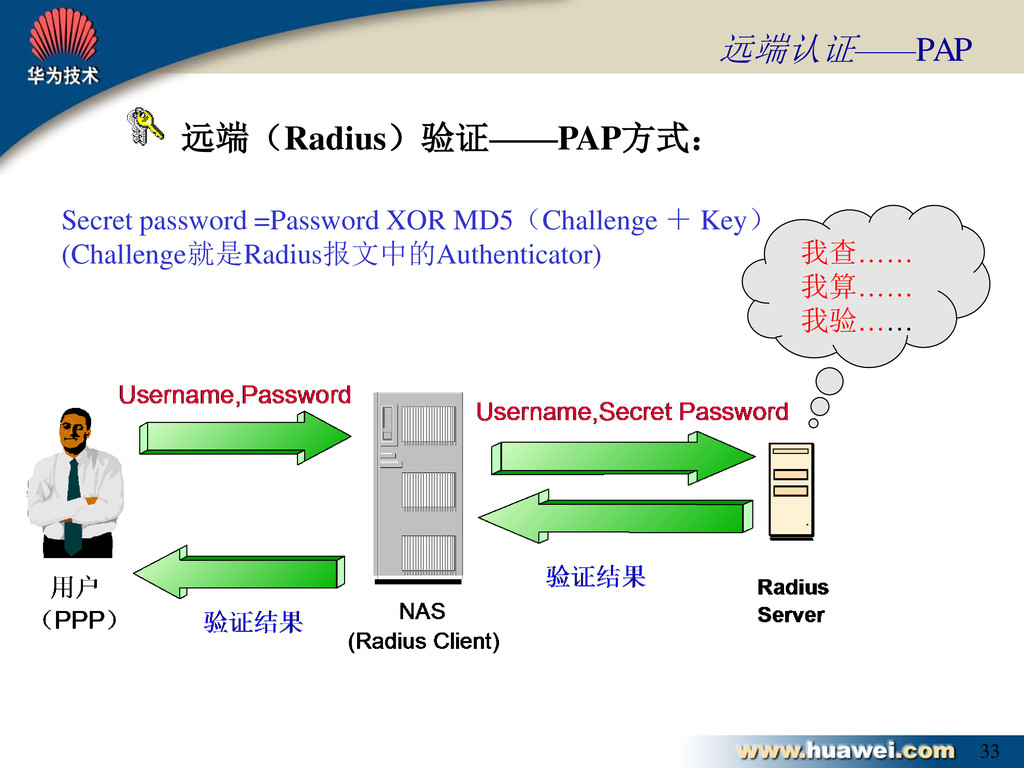
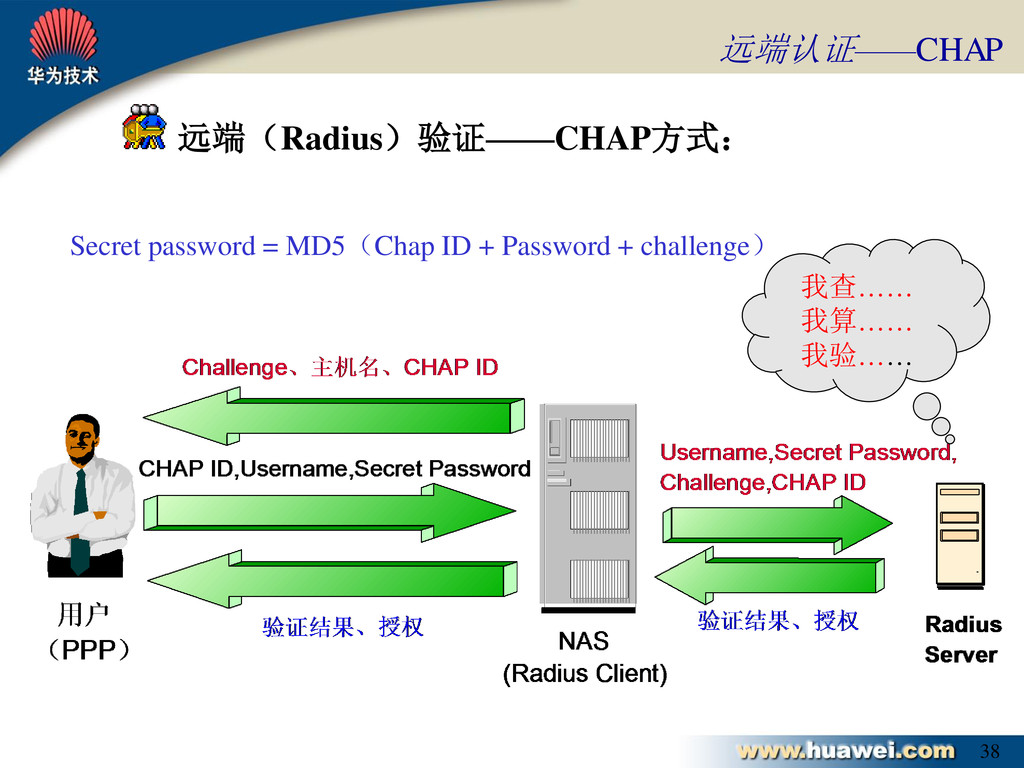
  3. 10 远端(Radius)验证——PAP方式: 远端认证——PAP Secret password =Password XOR MD5(Challenge + Key)

    (Challenge就是Radius报文中的Authenticator) 我查…… 我算…… 我验……
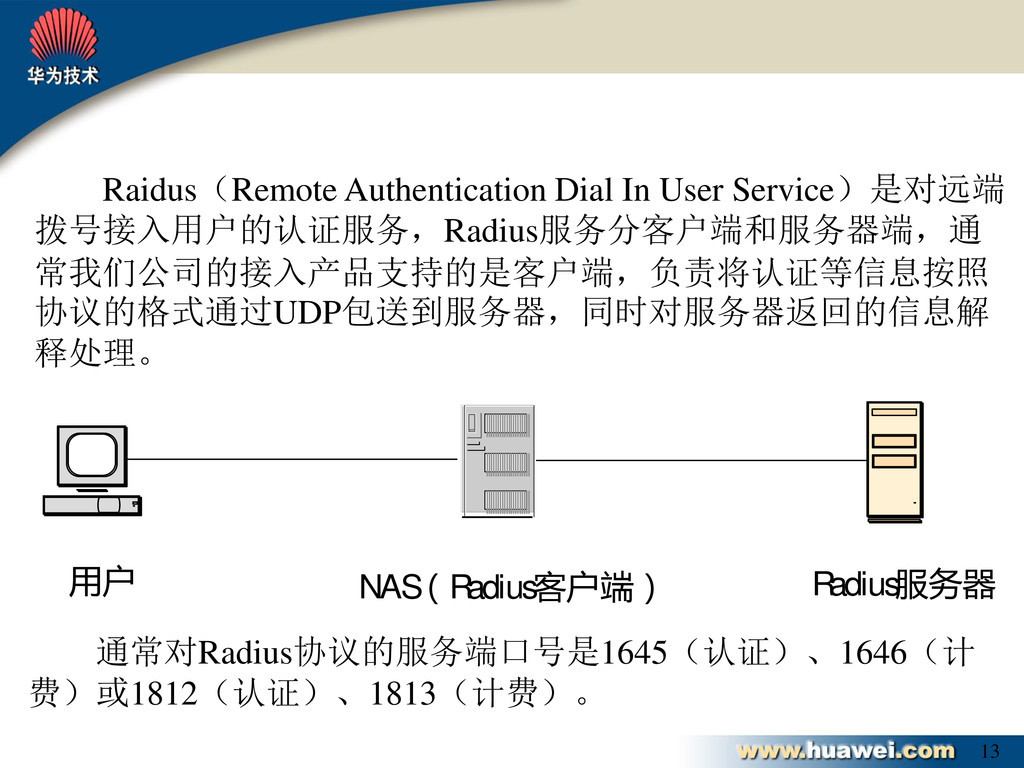
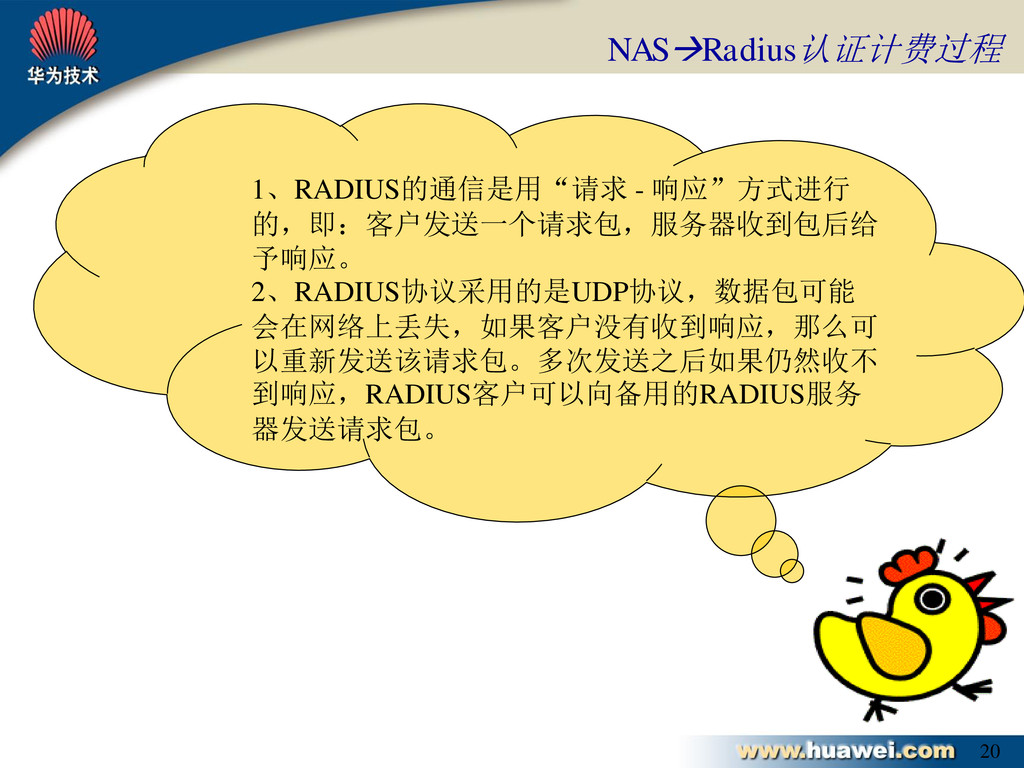
  4. 13 用户 NAS (R adius客户端) R adius服务器 Raidus(Remote Authentication Dial

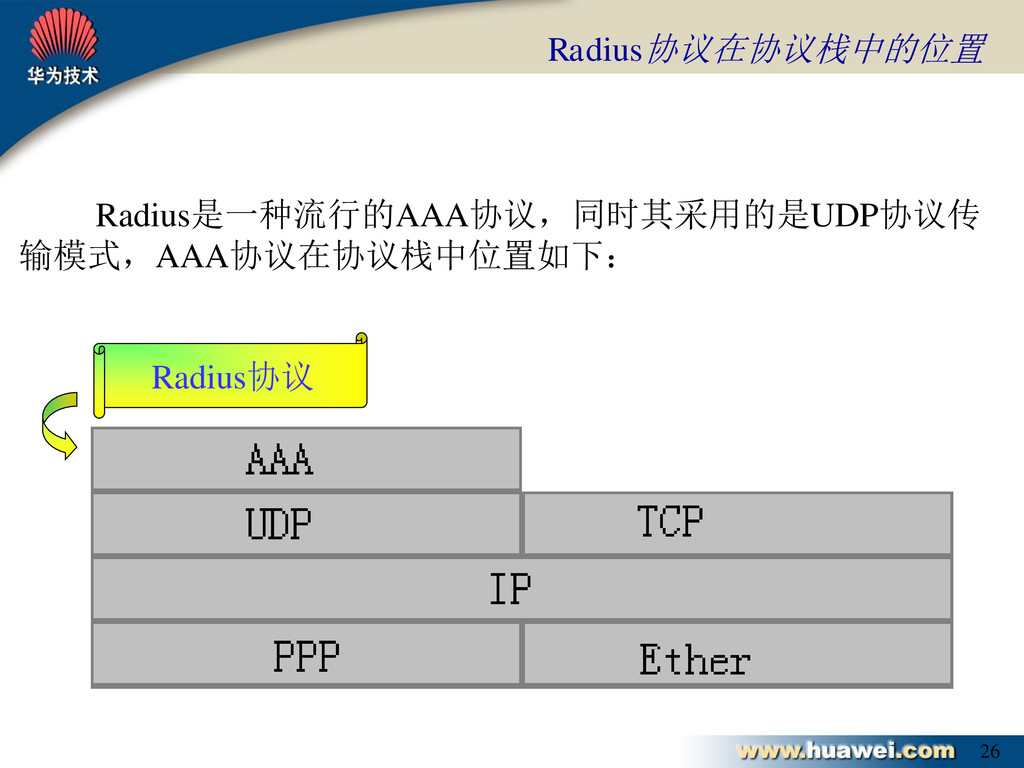
    In User Service)是对远端 拨号接入用户的认证服务,Radius服务分客户端和服务器端,通 常我们公司的接入产品支持的是客户端,负责将认证等信息按照 协议的格式通过UDP包送到服务器,同时对服务器返回的信息解 释处理。 通常对Radius协议的服务端口号是1645(认证)、1646(计 费)或1812(认证)、1813(计费)。
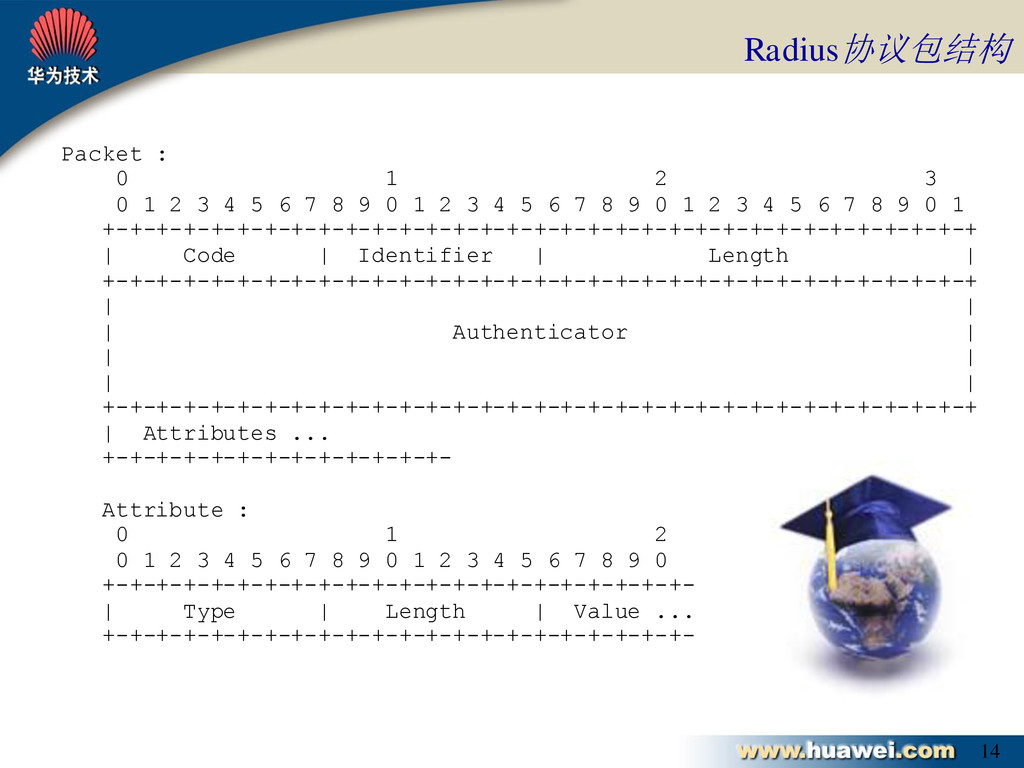
  5. 14 Packet : 0 1 2 3 0 1 2

    3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 1 +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+ | Code | Identifier | Length | +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+ | | | Authenticator | | | | | +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+ | Attributes ... +-+-+-+-+-+-+-+-+-+-+-+-+- Attribute : 0 1 2 0 1 2 3 4 5 6 7 8 9 0 1 2 3 4 5 6 7 8 9 0 +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+- | Type | Length | Value ... +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+- Radius协议包结构
  6. 16 1)Code:包的类型 包类型占1个字节,定义如下: 1 Access-Request——请求认证过程 2 Access-Accept——认证响应过程 3 Access-Reject——认证拒绝过程 4

    Accounting-Request——请求计费过程 5 Accounting-Response——计费响应过程 *12 Status-Server (experimental)——实验的 *13 Status-Client (experimental)——实验的 *255 Reserved——保留的 Radius协议包:code域
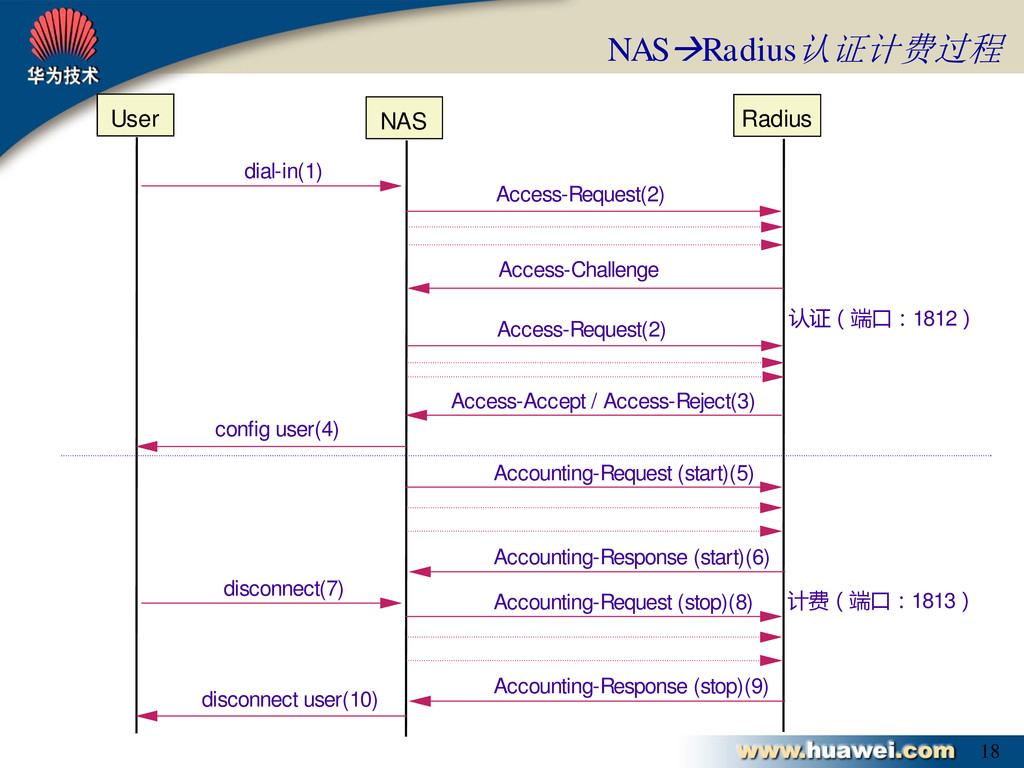
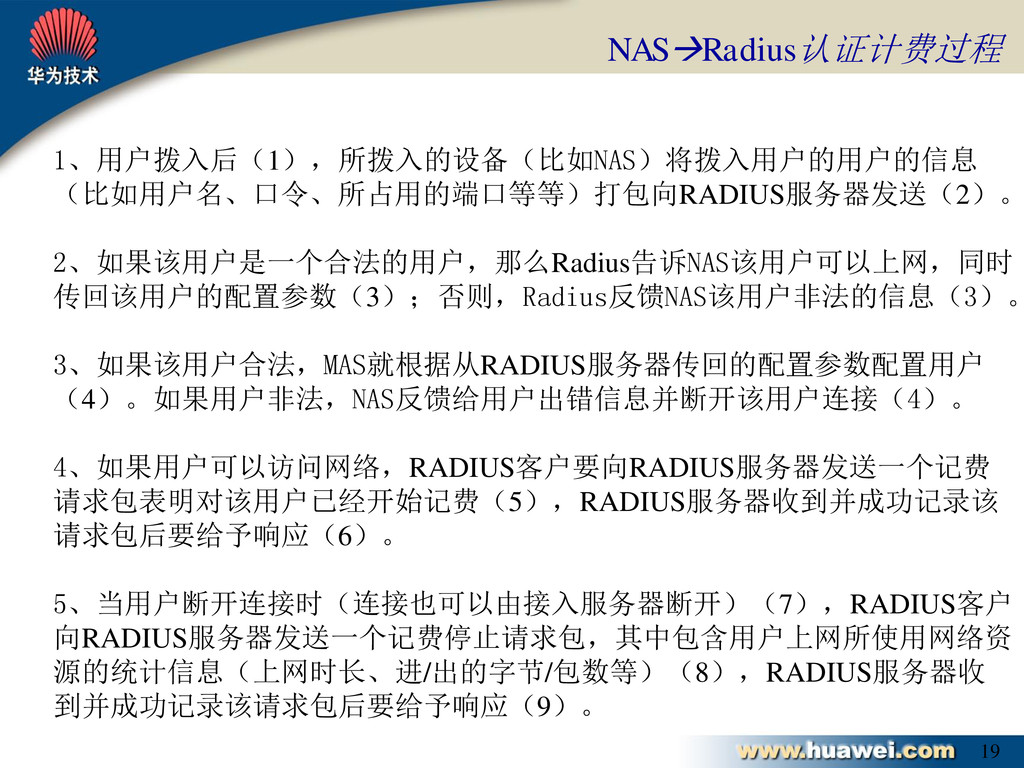
  7. 18 Radius Access-Request(2) Access-Accept / Access-Reject(3) 认证(端口:1812) Accounting-Request (start)(5) Accounting-Response

    (start)(6) Access-Request(2) Access-Challenge 计费(端口:1813) NAS User dial-in(1) config user(4) disconnect(7) Accounting-Request (stop)(8) Accounting-Response (stop)(9) disconnect user(10) NASRadius认证计费过程
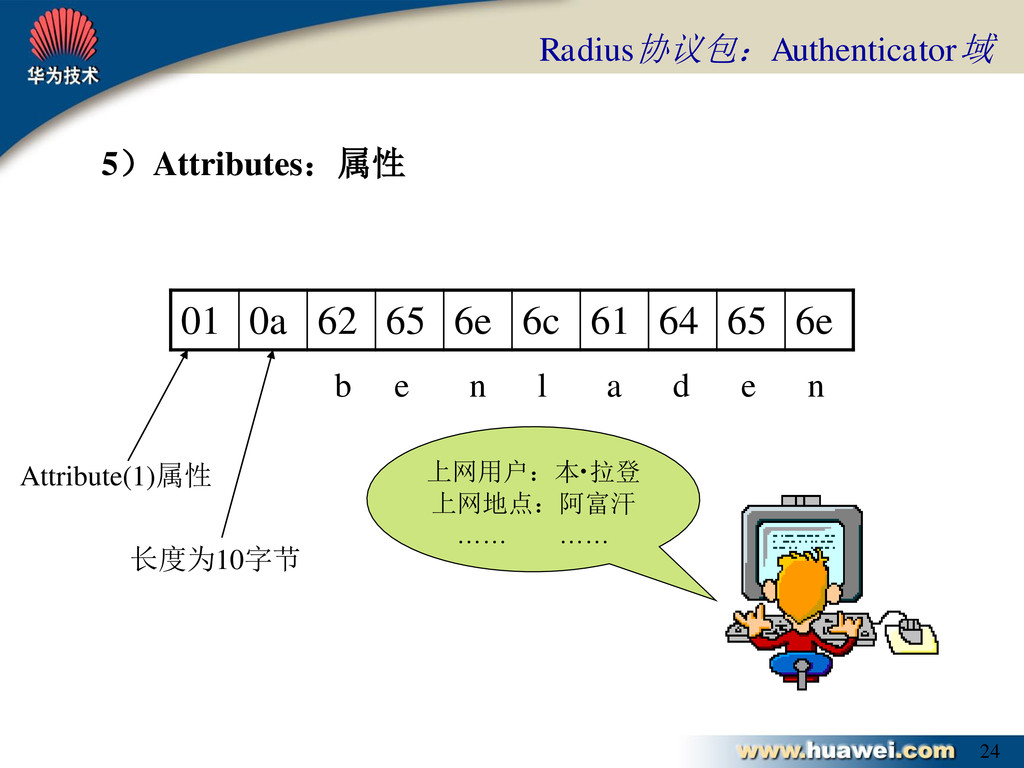
  8. 24 5)Attributes:属性 Radius协议包:Authenticator域 01 0a 62 65 6e 6c 61

    64 65 6e Attribute(1)属性 长度为10字节 b e n l a d e n 上网用户:本· 拉登 上网地点:阿富汗 …… ……
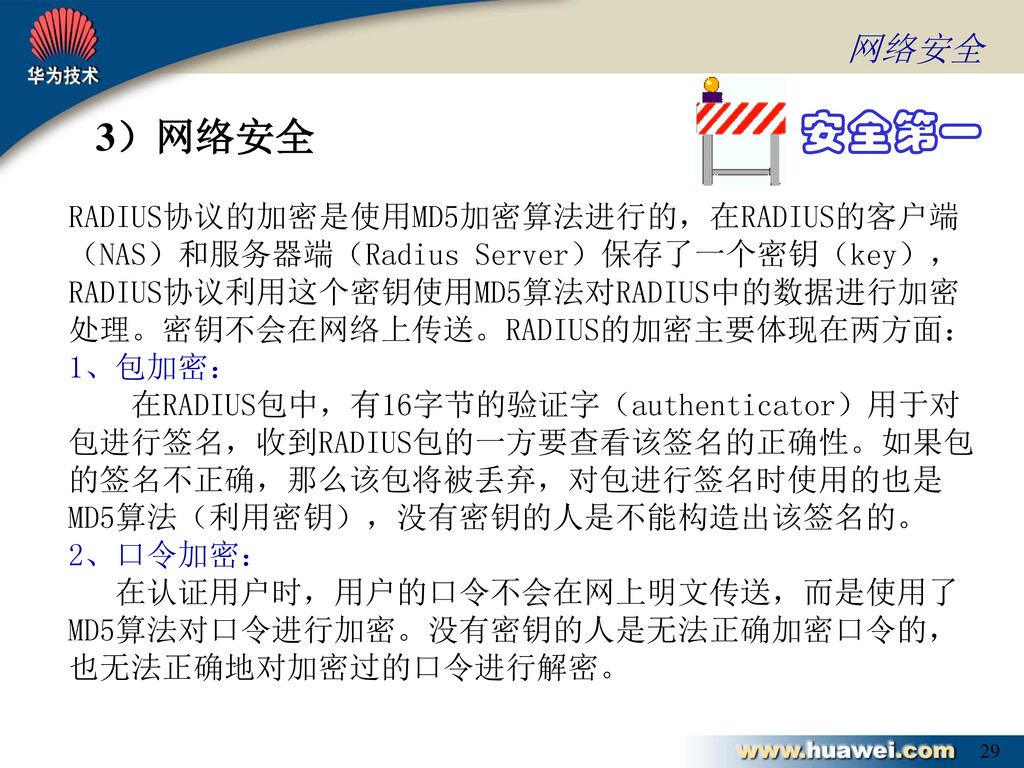
  9. 29 3)网络安全 RADIUS协议的加密是使用MD5加密算法进行的,在RADIUS的客户端 (NAS)和服务器端(Radius Server)保存了一个密钥(key), RADIUS协议利用这个密钥使用MD5算法对RADIUS中的数据进行加密 处理。密钥不会在网络上传送。RADIUS的加密主要体现在两方面: 1、包加密: 在RADIUS包中,有16字节的验证字(authenticator)用于对 包进行签名,收到RADIUS包的一方要查看该签名的正确性。如果包

    的签名不正确,那么该包将被丢弃,对包进行签名时使用的也是 MD5算法(利用密钥),没有密钥的人是不能构造出该签名的。 2、口令加密: 在认证用户时,用户的口令不会在网上明文传送,而是使用了 MD5算法对口令进行加密。没有密钥的人是无法正确加密口令的, 也无法正确地对加密过的口令进行解密。 网络安全 安全第一
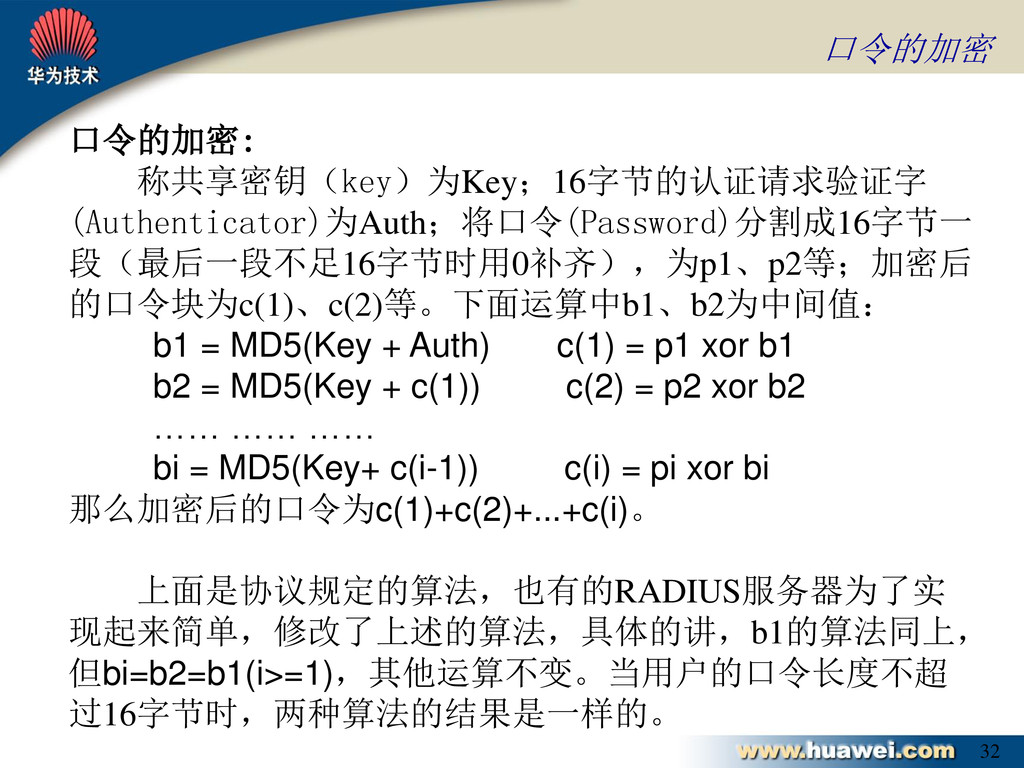
  10. 32 口令的加密: 称共享密钥(key)为Key;16字节的认证请求验证字 (Authenticator)为Auth;将口令(Password)分割成16字节一 段(最后一段不足16字节时用0补齐),为p1、p2等;加密后 的口令块为c(1)、c(2)等。下面运算中b1、b2为中间值: b1 = MD5(Key +

    Auth) c(1) = p1 xor b1 b2 = MD5(Key + c(1)) c(2) = p2 xor b2 …… …… …… bi = MD5(Key+ c(i-1)) c(i) = pi xor bi 那么加密后的口令为c(1)+c(2)+...+c(i)。 上面是协议规定的算法,也有的RADIUS服务器为了实 现起来简单,修改了上述的算法,具体的讲,b1的算法同上, 但bi=b2=b1(i>=1),其他运算不变。当用户的口令长度不超 过16字节时,两种算法的结果是一样的。 口令的加密
  11. 33 远端(Radius)验证——PAP方式: 远端认证——PAP Secret password =Password XOR MD5(Challenge + Key)

    (Challenge就是Radius报文中的Authenticator) 我查…… 我算…… 我验……
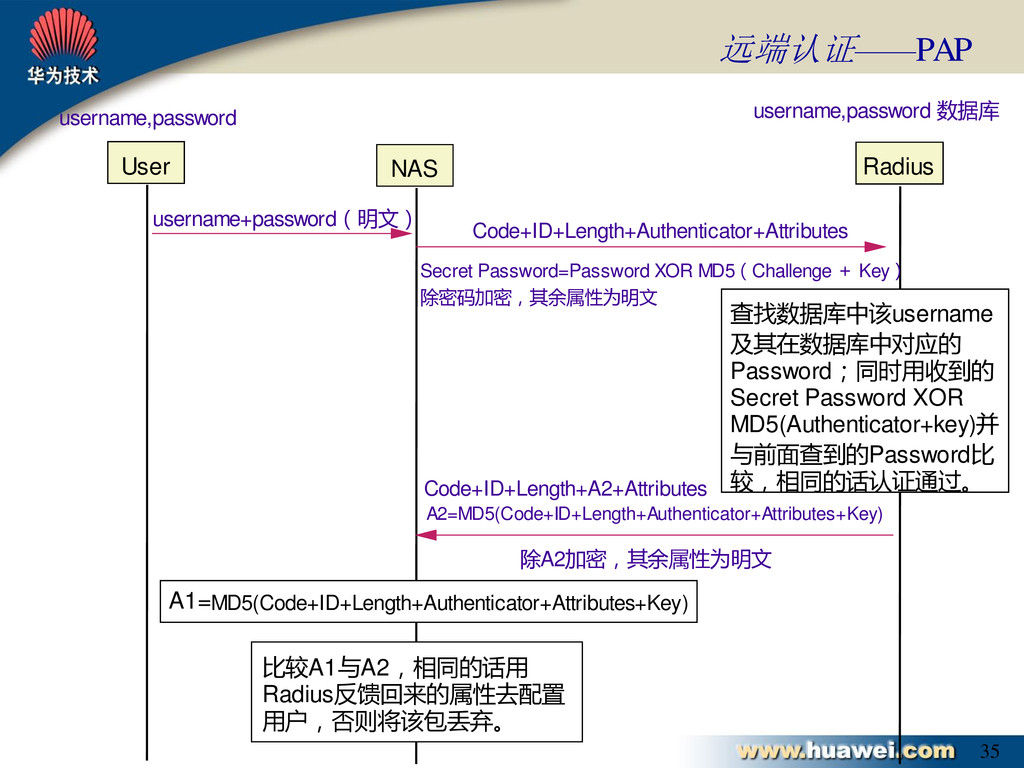
  12. 35 Radius Code+ID+Length+Authenticator+Attributes NAS User username+password(明文) A2=MD5(Code+ID+Length+Authenticator+Attributes+Key) username,password username,password 数据库

    Secret Password=Password XOR MD5(Challenge + Key) 查找数据库中该username 及其在数据库中对应的 Password;同时用收到的 Secret Password XOR MD5(Authenticator+key)并 与前面查到的Password比 较,相同的话认证通过。 A1=MD5(Code+ID+Length+Authenticator+Attributes+Key) 比较A1与A2,相同的话用 Radius反馈回来的属性去配置 用户,否则将该包丢弃。 Code+ID+Length+A2+Attributes 除A2加密,其余属性为明文 除密码加密,其余属性为明文 远端认证——PAP
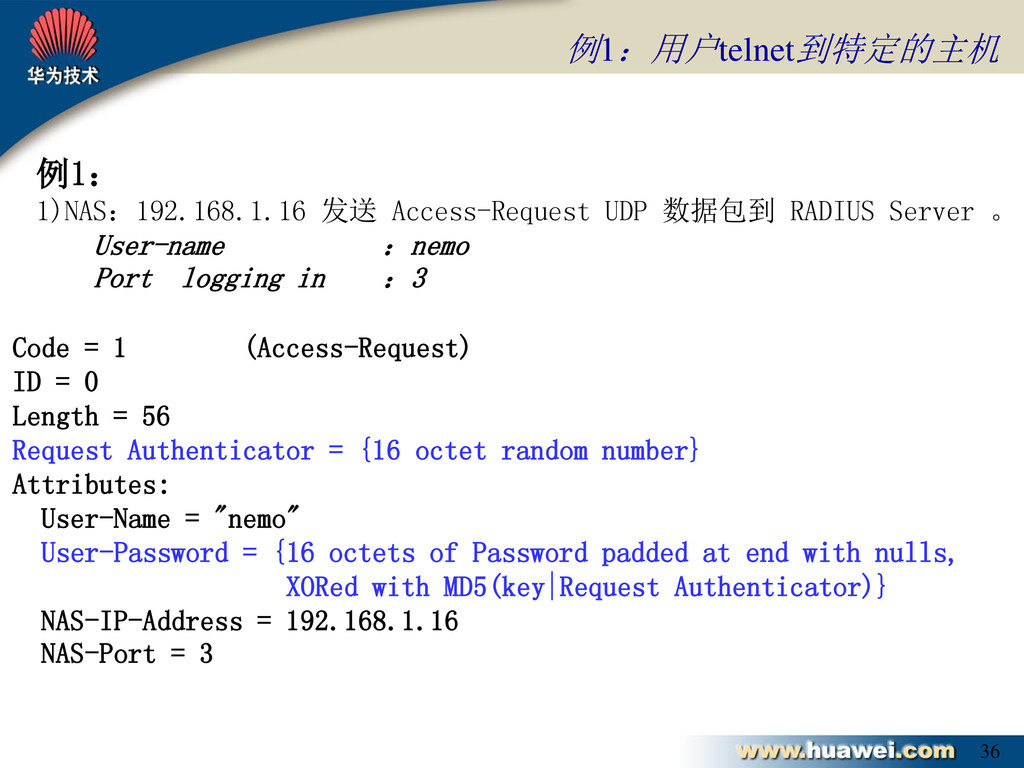
  13. 36 Code = 1 (Access-Request) ID = 0 Length =

    56 Request Authenticator = {16 octet random number} Attributes: User-Name = "nemo" User-Password = {16 octets of Password padded at end with nulls, XORed with MD5(key|Request Authenticator)} NAS-IP-Address = 192.168.1.16 NAS-Port = 3 例1:用户telnet到特定的主机 例1: 1)NAS:192.168.1.16 发送 Access-Request UDP 数据包到 RADIUS Server 。 User-name :nemo Port logging in :3
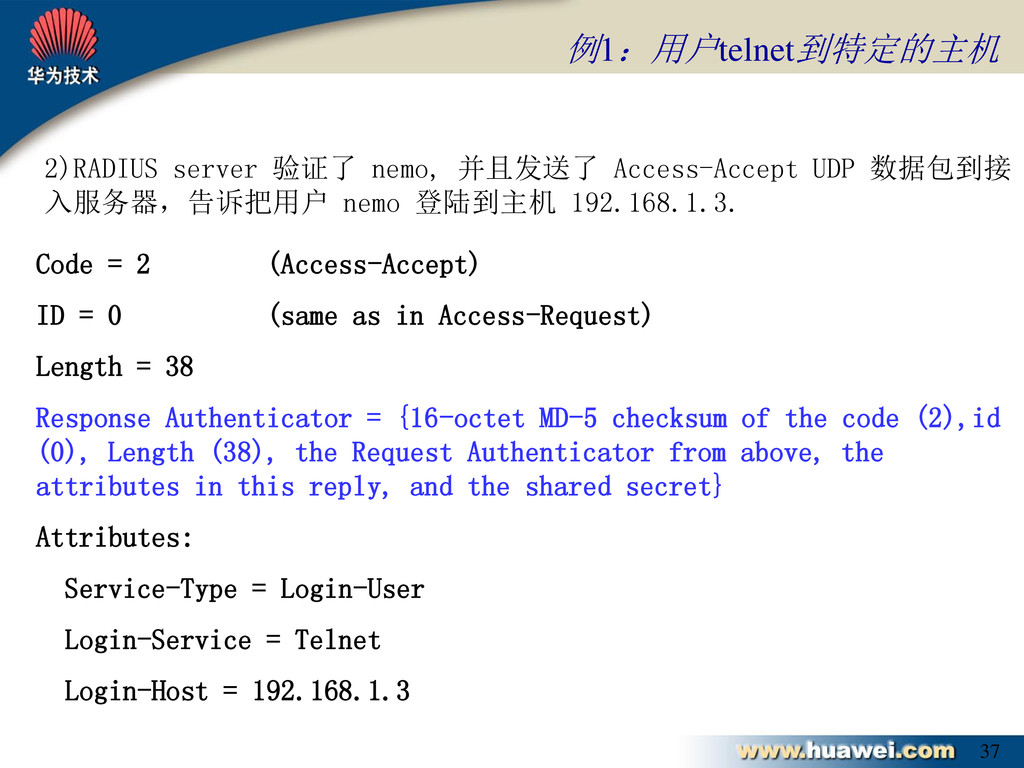
  14. 37 Code = 2 (Access-Accept) ID = 0 (same as

    in Access-Request) Length = 38 Response Authenticator = {16-octet MD-5 checksum of the code (2),id (0), Length (38), the Request Authenticator from above, the attributes in this reply, and the shared secret} Attributes: Service-Type = Login-User Login-Service = Telnet Login-Host = 192.168.1.3 2)RADIUS server 验证了 nemo, 并且发送了 Access-Accept UDP 数据包到接 入服务器,告诉把用户 nemo 登陆到主机 192.168.1.3. 例1:用户telnet到特定的主机
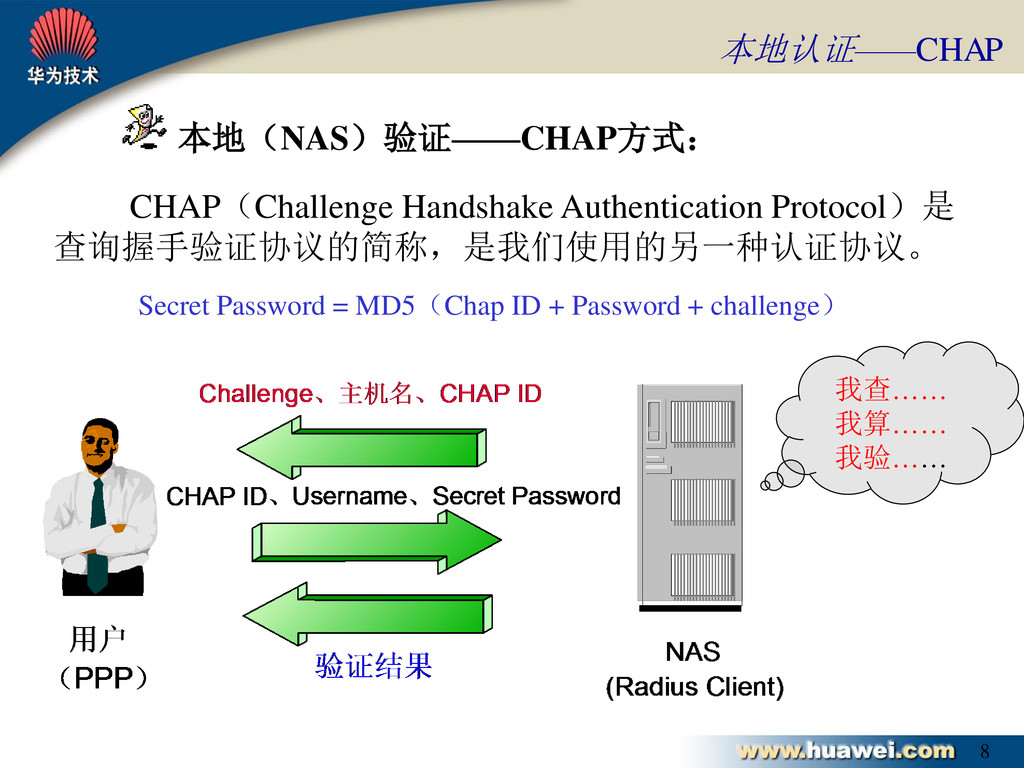
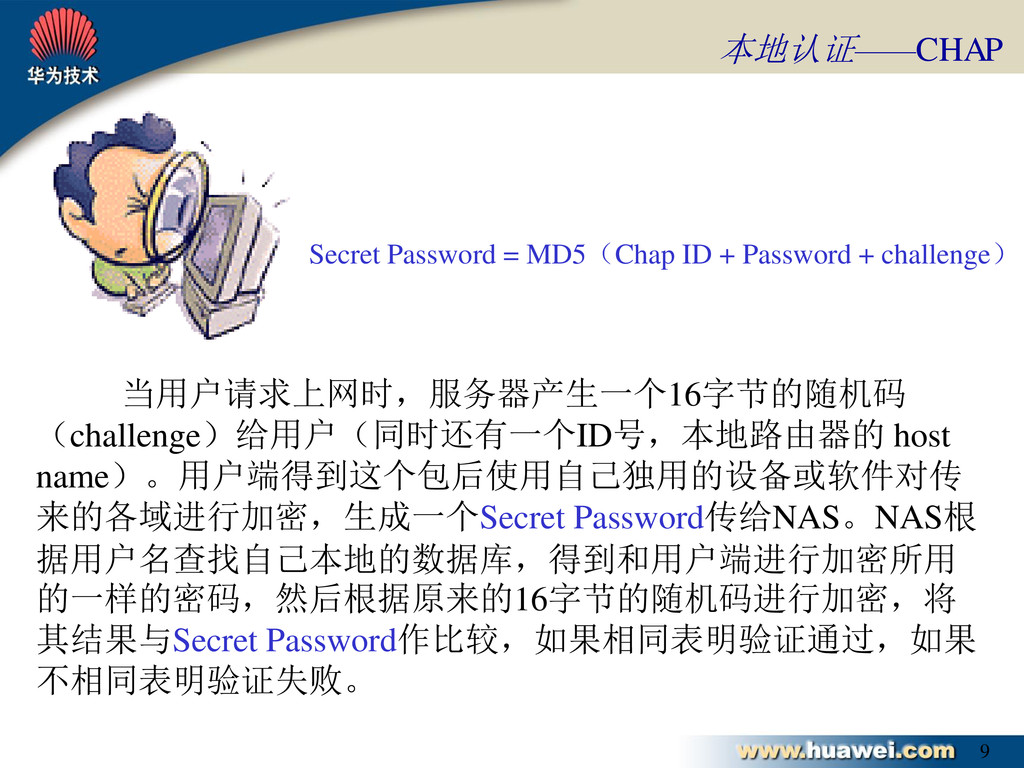
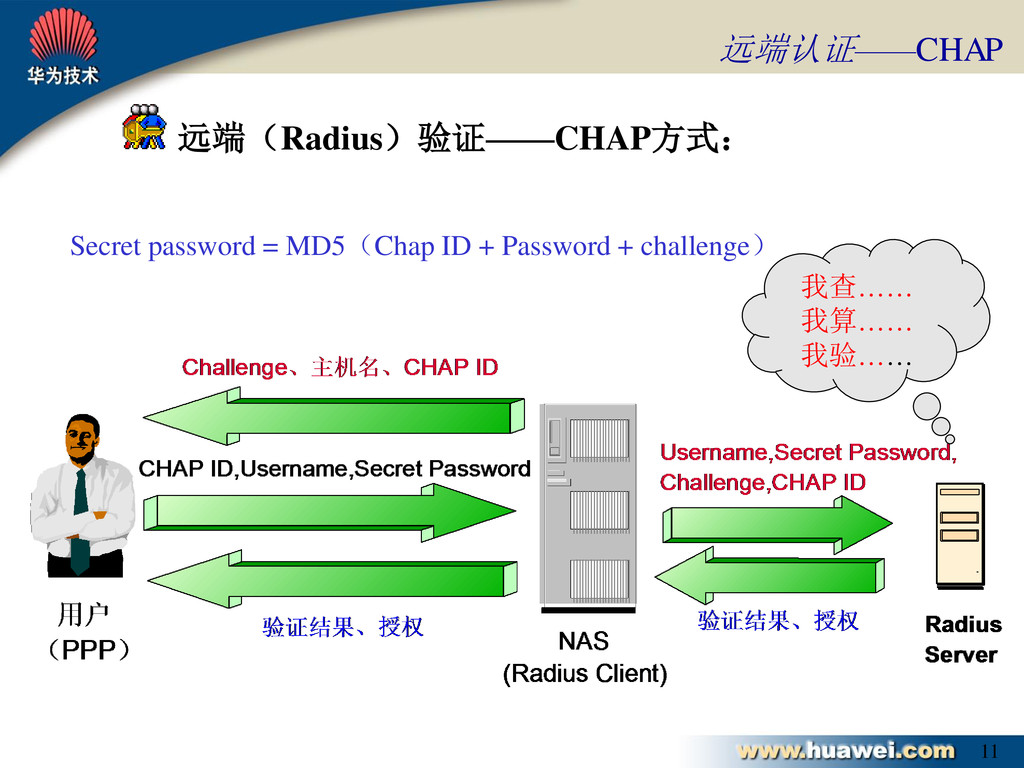
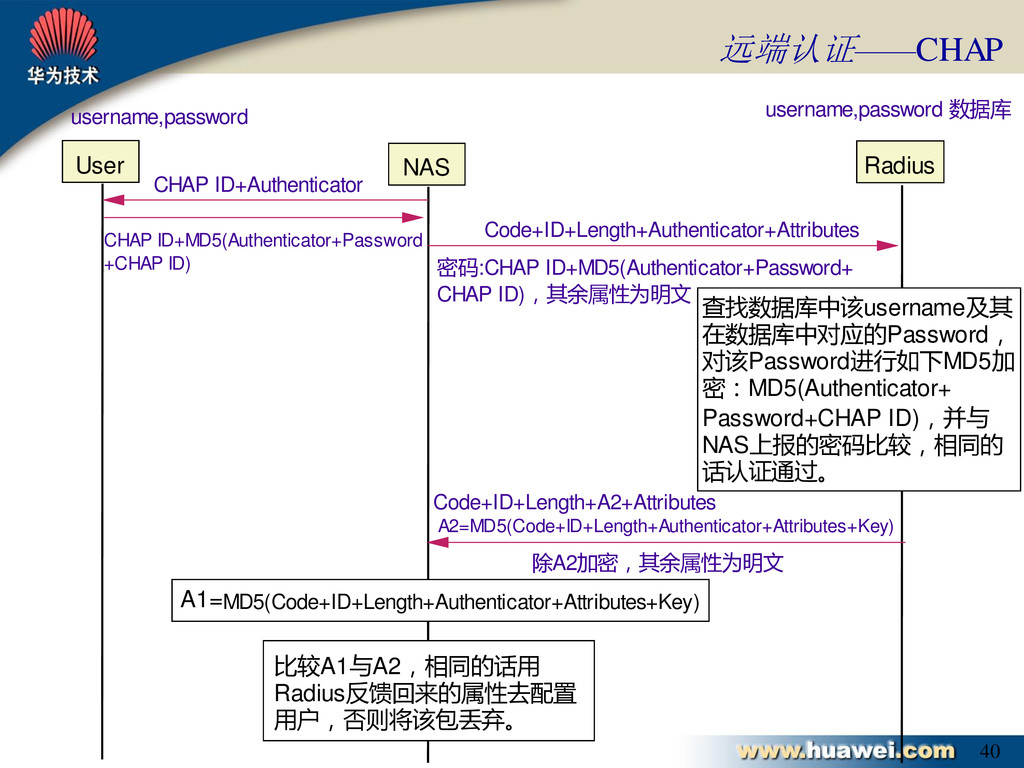
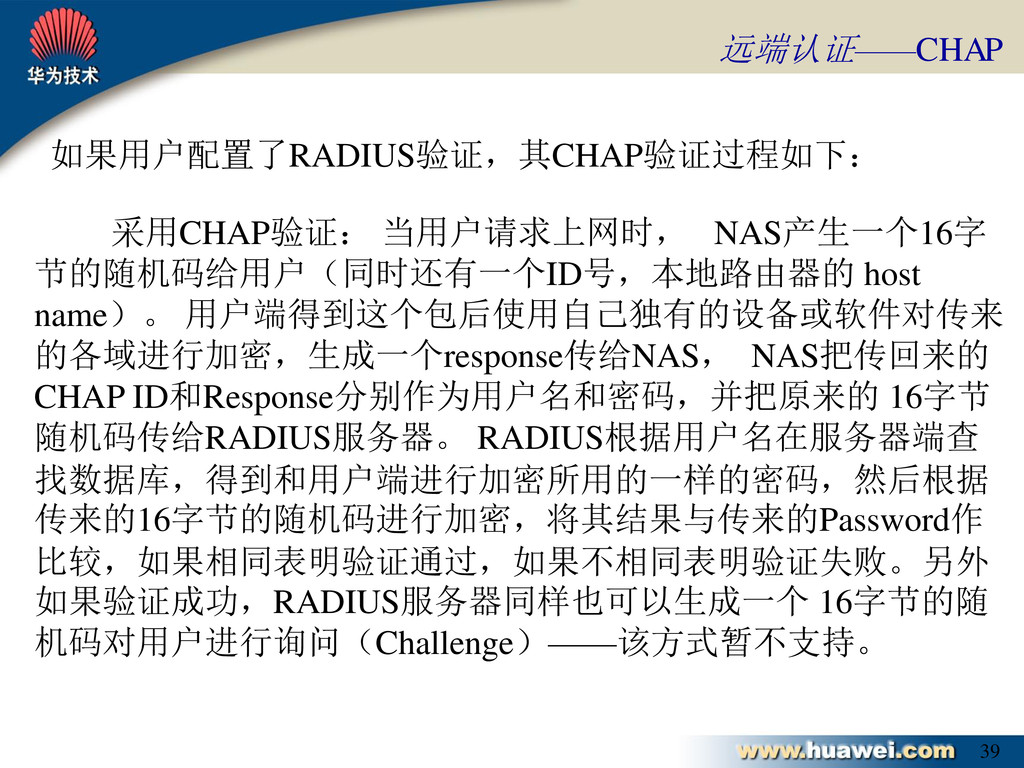
  15. 39 采用CHAP验证: 当用户请求上网时, NAS产生一个16字 节的随机码给用户(同时还有一个ID号,本地路由器的 host name)。 用户端得到这个包后使用自己独有的设备或软件对传来 的各域进行加密,生成一个response传给NAS, NAS把传回来的

    CHAP ID和Response分别作为用户名和密码,并把原来的 16字节 随机码传给RADIUS服务器。 RADIUS根据用户名在服务器端查 找数据库,得到和用户端进行加密所用的一样的密码,然后根据 传来的16字节的随机码进行加密,将其结果与传来的Password作 比较,如果相同表明验证通过,如果不相同表明验证失败。另外 如果验证成功,RADIUS服务器同样也可以生成一个 16字节的随 机码对用户进行询问(Challenge)——该方式暂不支持。 如果用户配置了RADIUS验证,其CHAP验证过程如下: 远端认证——CHAP
  16. 40 Radius Code+ID+Length+Authenticator+Attributes NAS User CHAP ID+MD5(Authenticator+Password +CHAP ID) A2=MD5(Code+ID+Length+Authenticator+Attributes+Key)

    username,password username,password 数据库 密码:CHAP ID+MD5(Authenticator+Password+ CHAP ID),其余属性为明文 查找数据库中该username及其 在数据库中对应的Password, 对该Password进行如下MD5加 密:MD5(Authenticator+ Password+CHAP ID),并与 NAS上报的密码比较,相同的 话认证通过。 A1=MD5(Code+ID+Length+Authenticator+Attributes+Key) 比较A1与A2,相同的话用 Radius反馈回来的属性去配置 用户,否则将该包丢弃。 Code+ID+Length+A2+Attributes 除A2加密,其余属性为明文 CHAP ID+Authenticator 远端认证——CHAP
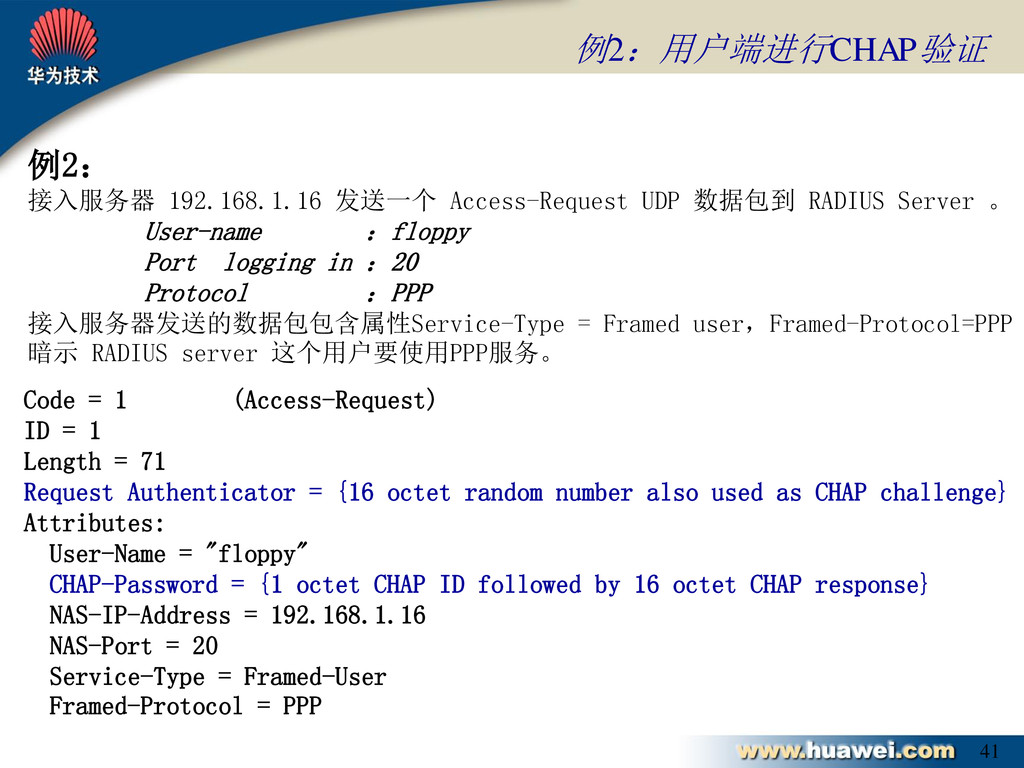
  17. 41 例2:用户端进行CHAP验证 Code = 1 (Access-Request) ID = 1 Length

    = 71 Request Authenticator = {16 octet random number also used as CHAP challenge} Attributes: User-Name = "floppy" CHAP-Password = {1 octet CHAP ID followed by 16 octet CHAP response} NAS-IP-Address = 192.168.1.16 NAS-Port = 20 Service-Type = Framed-User Framed-Protocol = PPP 例2: 接入服务器 192.168.1.16 发送一个 Access-Request UDP 数据包到 RADIUS Server 。 User-name :floppy Port logging in :20 Protocol :PPP 接入服务器发送的数据包包含属性Service-Type = Framed user,Framed-Protocol=PPP 暗示 RADIUS server 这个用户要使用PPP服务。
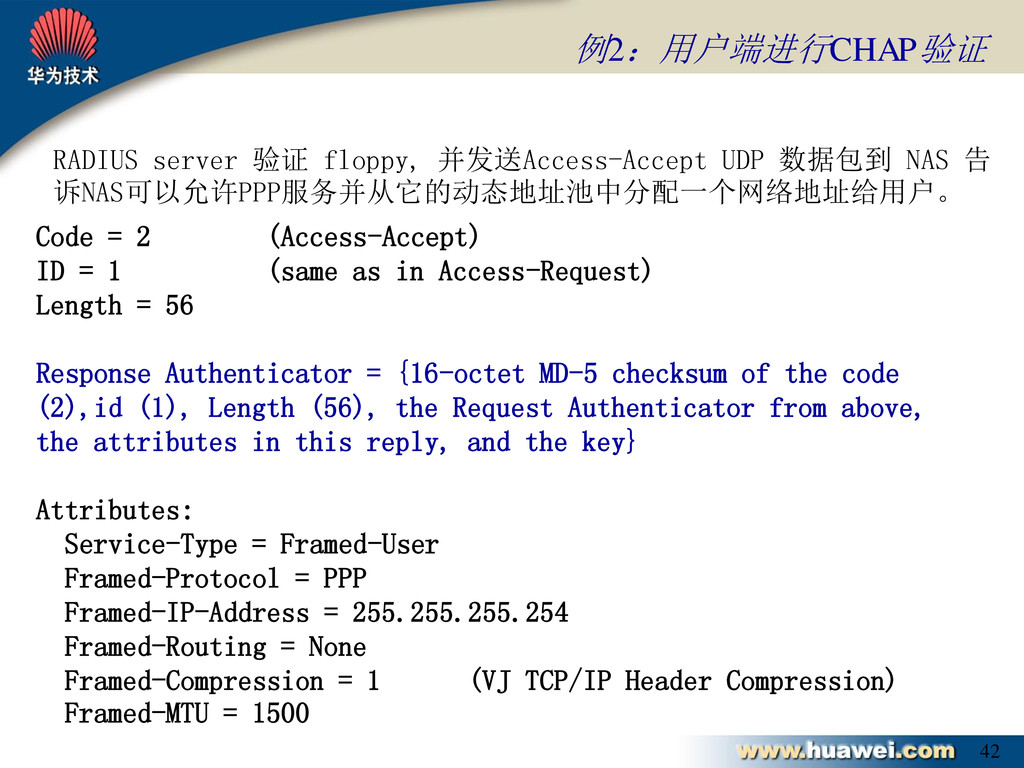
  18. 42 Code = 2 (Access-Accept) ID = 1 (same as

    in Access-Request) Length = 56 Response Authenticator = {16-octet MD-5 checksum of the code (2),id (1), Length (56), the Request Authenticator from above, the attributes in this reply, and the key} Attributes: Service-Type = Framed-User Framed-Protocol = PPP Framed-IP-Address = 255.255.255.254 Framed-Routing = None Framed-Compression = 1 (VJ TCP/IP Header Compression) Framed-MTU = 1500 RADIUS server 验证 floppy, 并发送Access-Accept UDP 数据包到 NAS 告 诉NAS可以允许PPP服务并从它的动态地址池中分配一个网络地址给用户。 例2:用户端进行CHAP验证
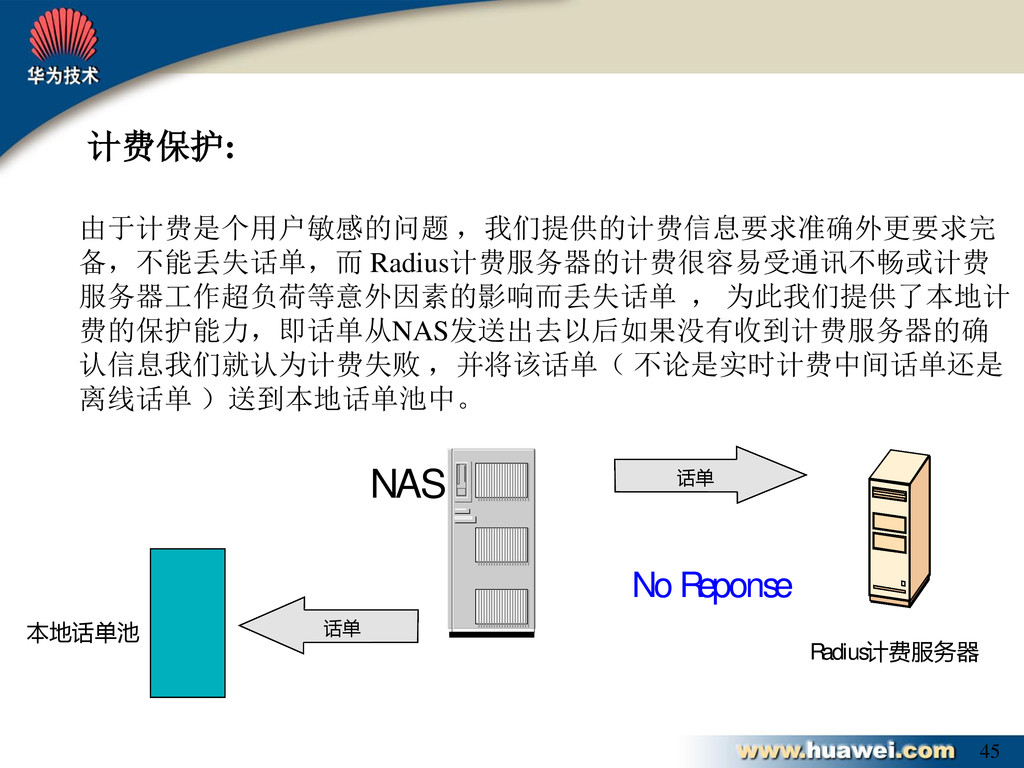
  19. 45 NAS Radius计费服务器 本地话单池 No R eponse 话单 话单 计费保护:

    由于计费是个用户敏感的问题 ,我们提供的计费信息要求准确外更要求完 备,不能丢失话单,而 Radius计费服务器的计费很容易受通讯不畅或计费 服务器工作超负荷等意外因素的影响而丢失话单 , 为此我们提供了本地计 费的保护能力,即话单从NAS发送出去以后如果没有收到计费服务器的确 认信息我们就认为计费失败 ,并将该话单( 不论是实时计费中间话单还是 离线话单 )送到本地话单池中。
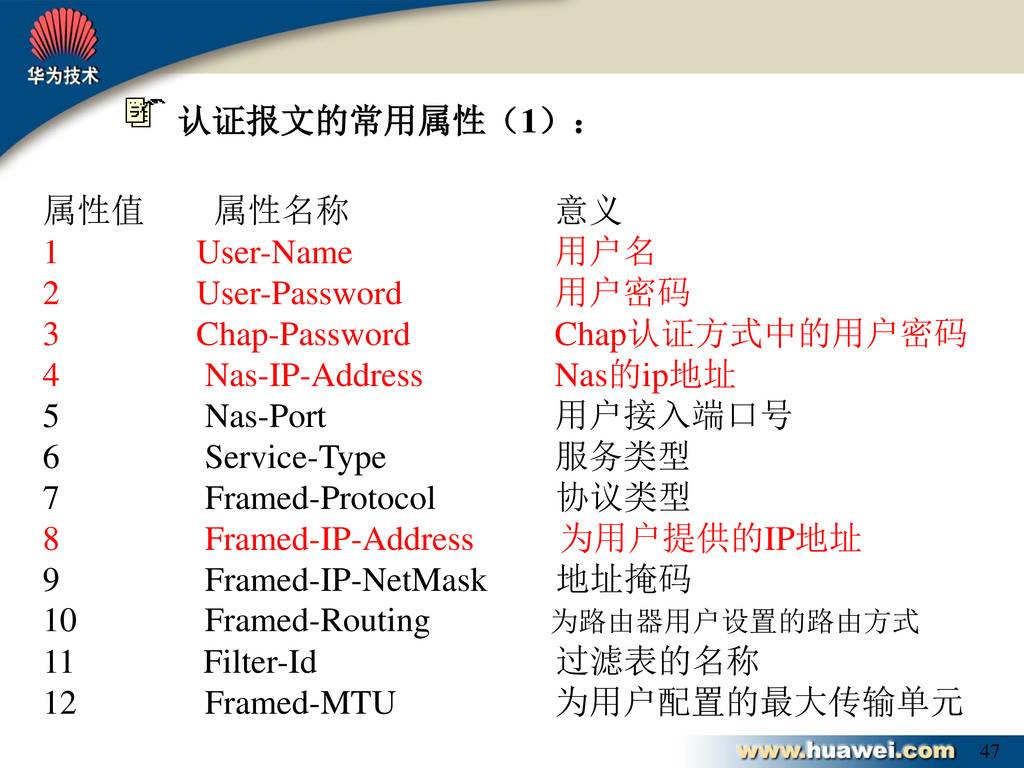
  20. 47 属性值 属性名称 意义 1 User-Name 用户名 2 User-Password 用户密码

    3 Chap-Password Chap认证方式中的用户密码 4 Nas-IP-Address Nas的ip地址 5 Nas-Port 用户接入端口号 6 Service-Type 服务类型 7 Framed-Protocol 协议类型 8 Framed-IP-Address 为用户提供的IP地址 9 Framed-IP-NetMask 地址掩码 10 Framed-Routing 为路由器用户设置的路由方式 11 Filter-Id 过滤表的名称 12 Framed-MTU 为用户配置的最大传输单元 认证报文的常用属性(1):
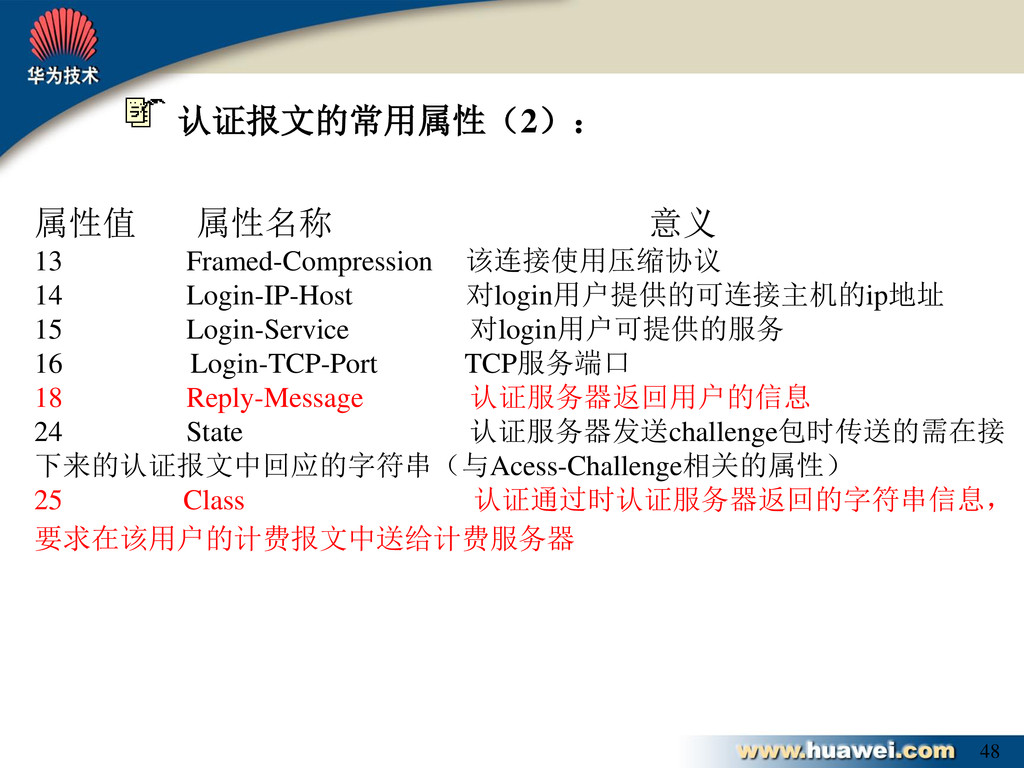
  21. 48 属性值 属性名称 意义 13 Framed-Compression 该连接使用压缩协议 14 Login-IP-Host 对login用户提供的可连接主机的ip地址

    15 Login-Service 对login用户可提供的服务 16 Login-TCP-Port TCP服务端口 18 Reply-Message 认证服务器返回用户的信息 24 State 认证服务器发送challenge包时传送的需在接 下来的认证报文中回应的字符串(与Acess-Challenge相关的属性) 25 Class 认证通过时认证服务器返回的字符串信息, 要求在该用户的计费报文中送给计费服务器 认证报文的常用属性(2):
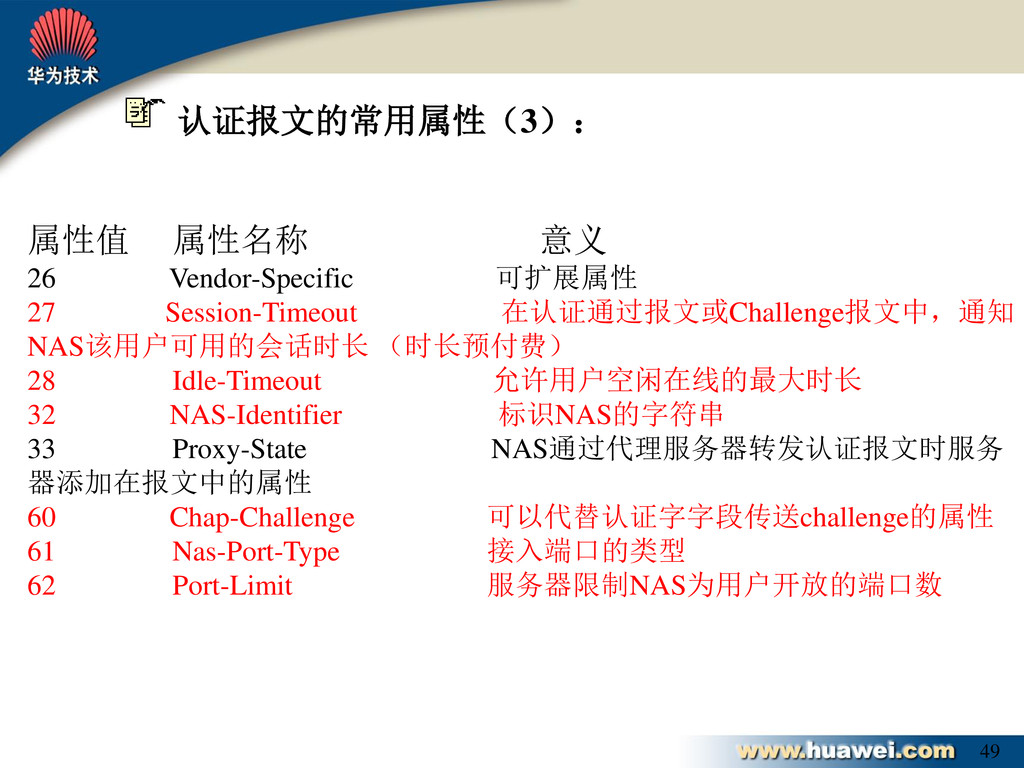
  22. 49 属性值 属性名称 意义 26 Vendor-Specific 可扩展属性 27 Session-Timeout 在认证通过报文或Challenge报文中,通知

    NAS该用户可用的会话时长 (时长预付费) 28 Idle-Timeout 允许用户空闲在线的最大时长 32 NAS-Identifier 标识NAS的字符串 33 Proxy-State NAS通过代理服务器转发认证报文时服务 器添加在报文中的属性 60 Chap-Challenge 可以代替认证字字段传送challenge的属性 61 Nas-Port-Type 接入端口的类型 62 Port-Limit 服务器限制NAS为用户开放的端口数 认证报文的常用属性(3):
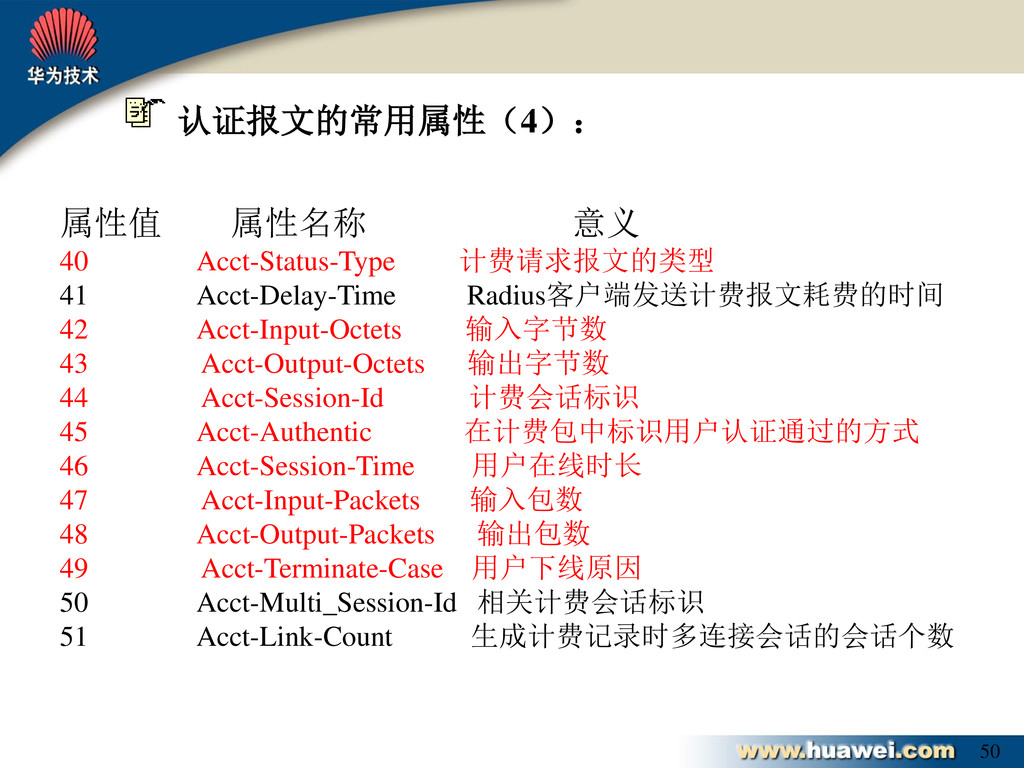
  23. 50 属性值 属性名称 意义 40 Acct-Status-Type 计费请求报文的类型 41 Acct-Delay-Time Radius客户端发送计费报文耗费的时间

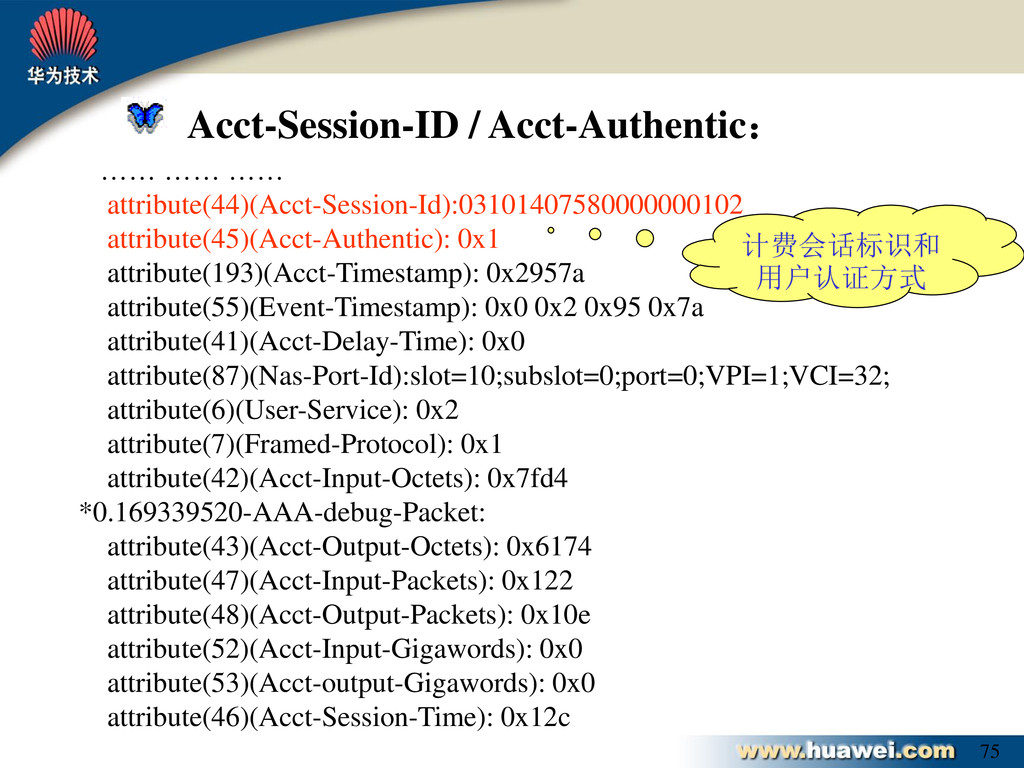
    42 Acct-Input-Octets 输入字节数 43 Acct-Output-Octets 输出字节数 44 Acct-Session-Id 计费会话标识 45 Acct-Authentic 在计费包中标识用户认证通过的方式 46 Acct-Session-Time 用户在线时长 47 Acct-Input-Packets 输入包数 48 Acct-Output-Packets 输出包数 49 Acct-Terminate-Case 用户下线原因 50 Acct-Multi_Session-Id 相关计费会话标识 51 Acct-Link-Count 生成计费记录时多连接会话的会话个数 认证报文的常用属性(4):
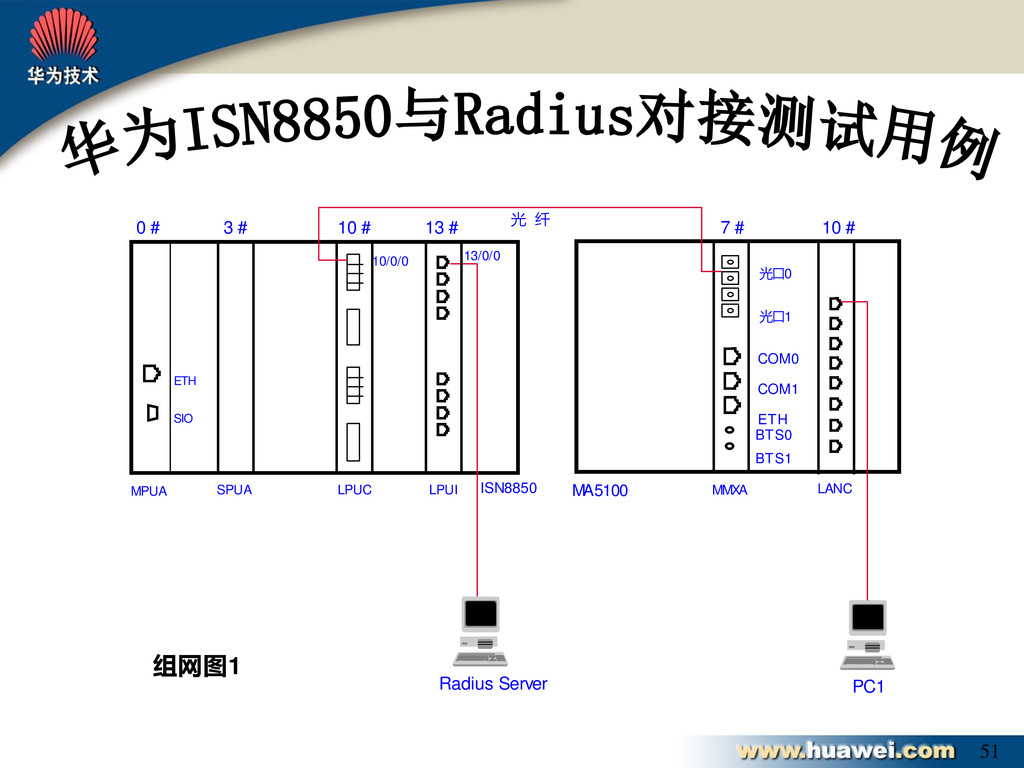
  24. 51 光口0 光口1 BTS0 BTS1 COM0 COM1 ETH MMXA MA5100

    光 纤 LPUC ISN8850 ETH SIO MPUA Radius Server SPUA 0 # 3 # 10 # 7 # 13 # LPUI 组网图1 10/0/0 LANC 10 # PC1 13/0/0
  25. 53

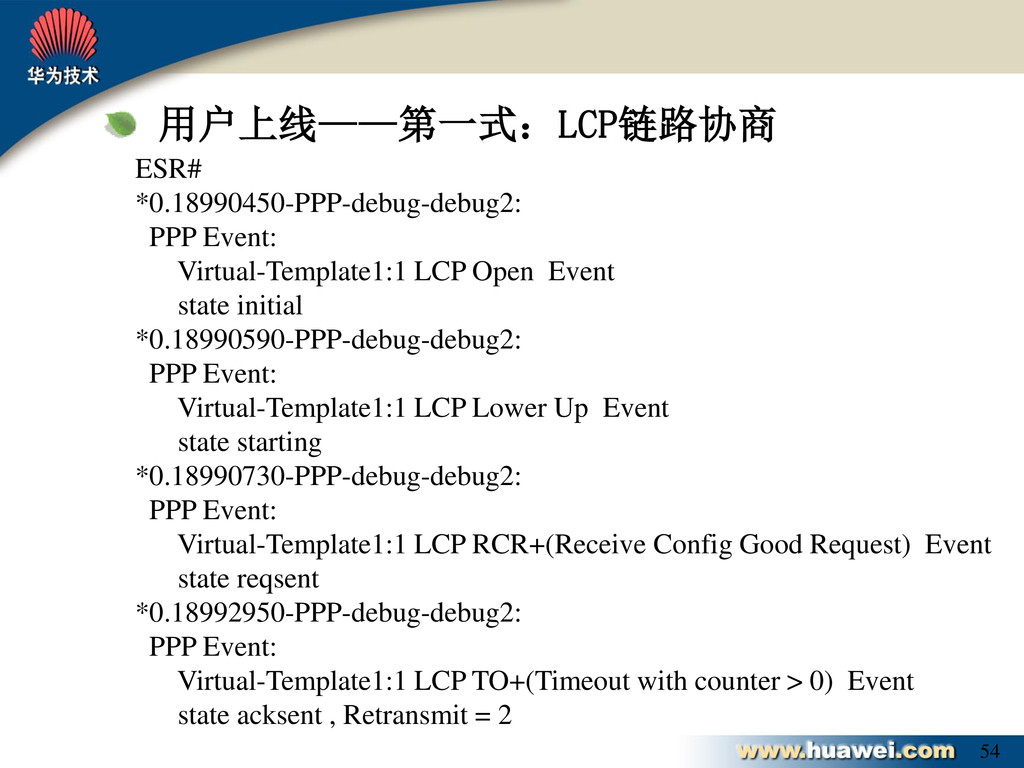
  26. 54 用户上线——第一式:LCP链路协商 ESR# *0.18990450-PPP-debug-debug2: PPP Event: Virtual-Template1:1 LCP Open Event

    state initial *0.18990590-PPP-debug-debug2: PPP Event: Virtual-Template1:1 LCP Lower Up Event state starting *0.18990730-PPP-debug-debug2: PPP Event: Virtual-Template1:1 LCP RCR+(Receive Config Good Request) Event state reqsent *0.18992950-PPP-debug-debug2: PPP Event: Virtual-Template1:1 LCP TO+(Timeout with counter > 0) Event state acksent , Retransmit = 2
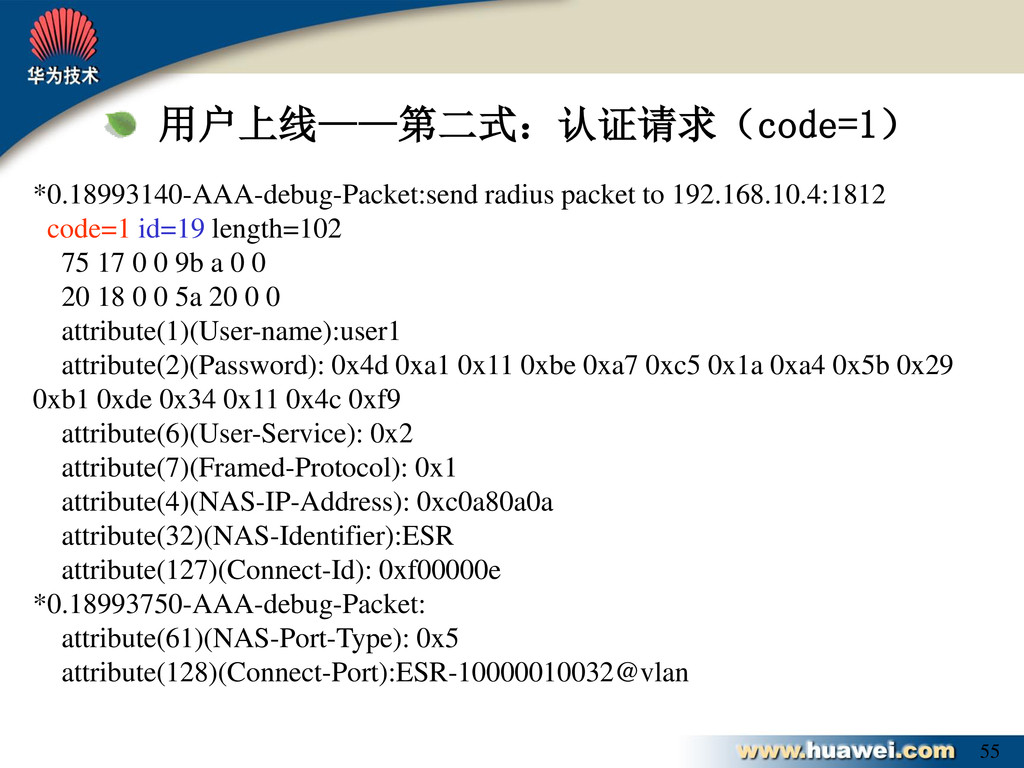
  27. 55 *0.18993140-AAA-debug-Packet:send radius packet to 192.168.10.4:1812 code=1 id=19 length=102 75

    17 0 0 9b a 0 0 20 18 0 0 5a 20 0 0 attribute(1)(User-name):user1 attribute(2)(Password): 0x4d 0xa1 0x11 0xbe 0xa7 0xc5 0x1a 0xa4 0x5b 0x29 0xb1 0xde 0x34 0x11 0x4c 0xf9 attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1 attribute(4)(NAS-IP-Address): 0xc0a80a0a attribute(32)(NAS-Identifier):ESR attribute(127)(Connect-Id): 0xf00000e *0.18993750-AAA-debug-Packet: attribute(61)(NAS-Port-Type): 0x5 attribute(128)(Connect-Port):ESR-10000010032@vlan 用户上线——第二式:认证请求(code=1)
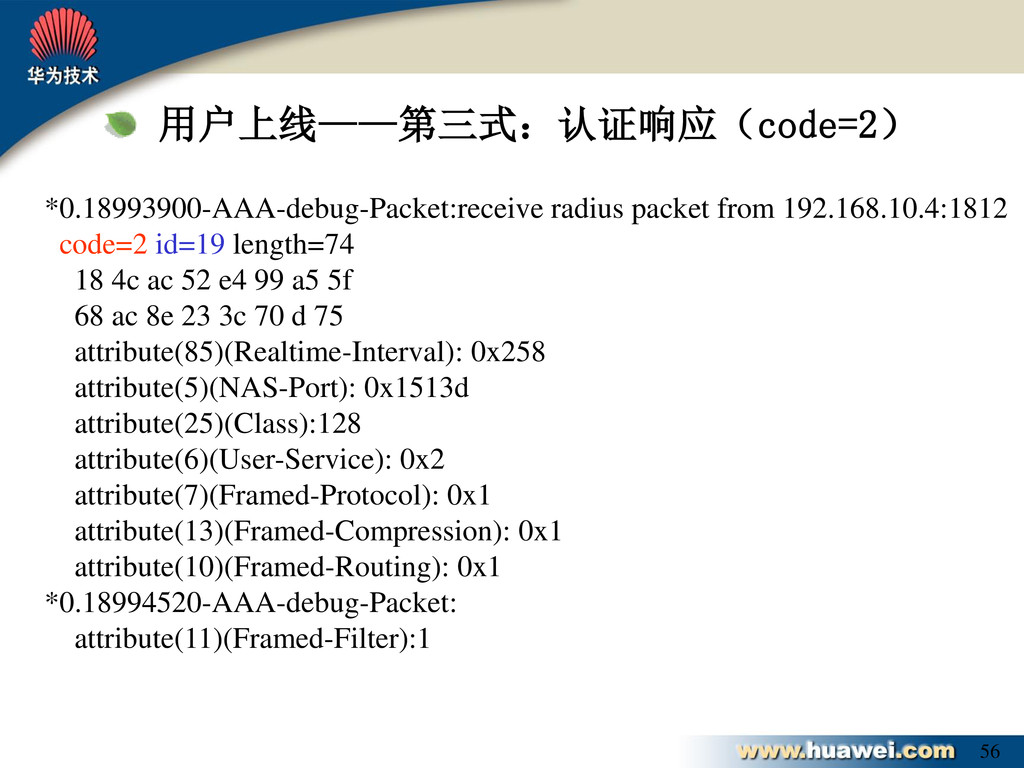
  28. 56 用户上线——第三式:认证响应(code=2) *0.18993900-AAA-debug-Packet:receive radius packet from 192.168.10.4:1812 code=2 id=19 length=74

    18 4c ac 52 e4 99 a5 5f 68 ac 8e 23 3c 70 d 75 attribute(85)(Realtime-Interval): 0x258 attribute(5)(NAS-Port): 0x1513d attribute(25)(Class):128 attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1 attribute(13)(Framed-Compression): 0x1 attribute(10)(Framed-Routing): 0x1 *0.18994520-AAA-debug-Packet: attribute(11)(Framed-Filter):1
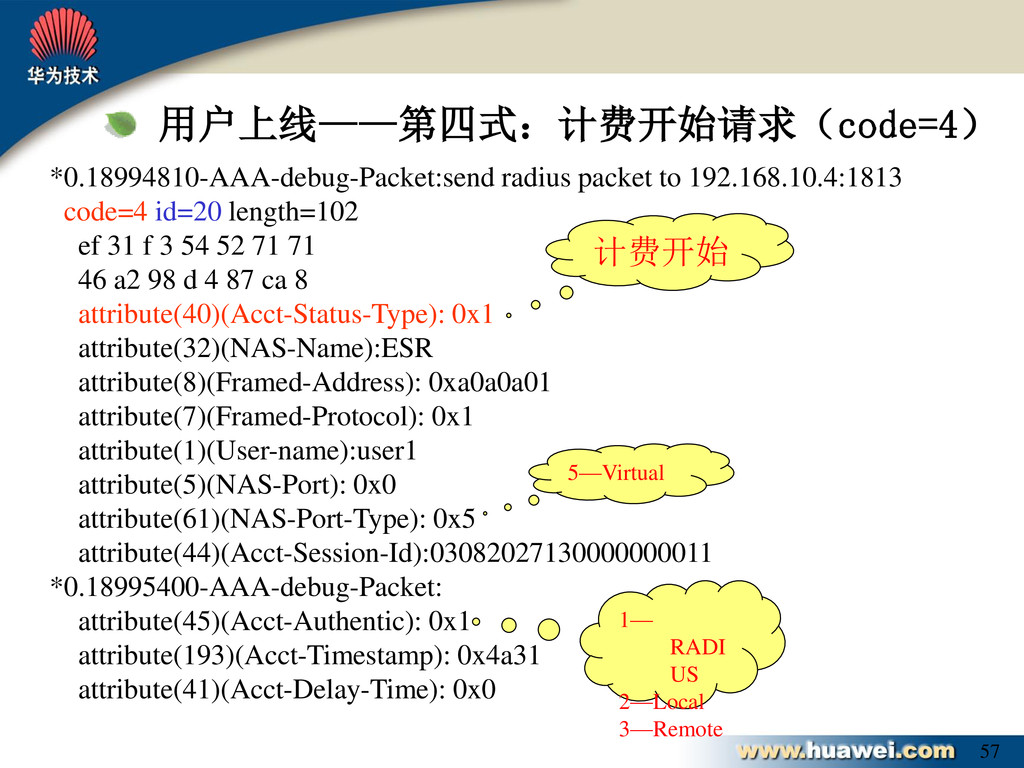
  29. 57 用户上线——第四式:计费开始请求(code=4) *0.18994810-AAA-debug-Packet:send radius packet to 192.168.10.4:1813 code=4 id=20 length=102

    ef 31 f 3 54 52 71 71 46 a2 98 d 4 87 ca 8 attribute(40)(Acct-Status-Type): 0x1 attribute(32)(NAS-Name):ESR attribute(8)(Framed-Address): 0xa0a0a01 attribute(7)(Framed-Protocol): 0x1 attribute(1)(User-name):user1 attribute(5)(NAS-Port): 0x0 attribute(61)(NAS-Port-Type): 0x5 attribute(44)(Acct-Session-Id):03082027130000000011 *0.18995400-AAA-debug-Packet: attribute(45)(Acct-Authentic): 0x1 attribute(193)(Acct-Timestamp): 0x4a31 attribute(41)(Acct-Delay-Time): 0x0 计费开始 1— RADI US 2—Local 3—Remote 5—Virtual
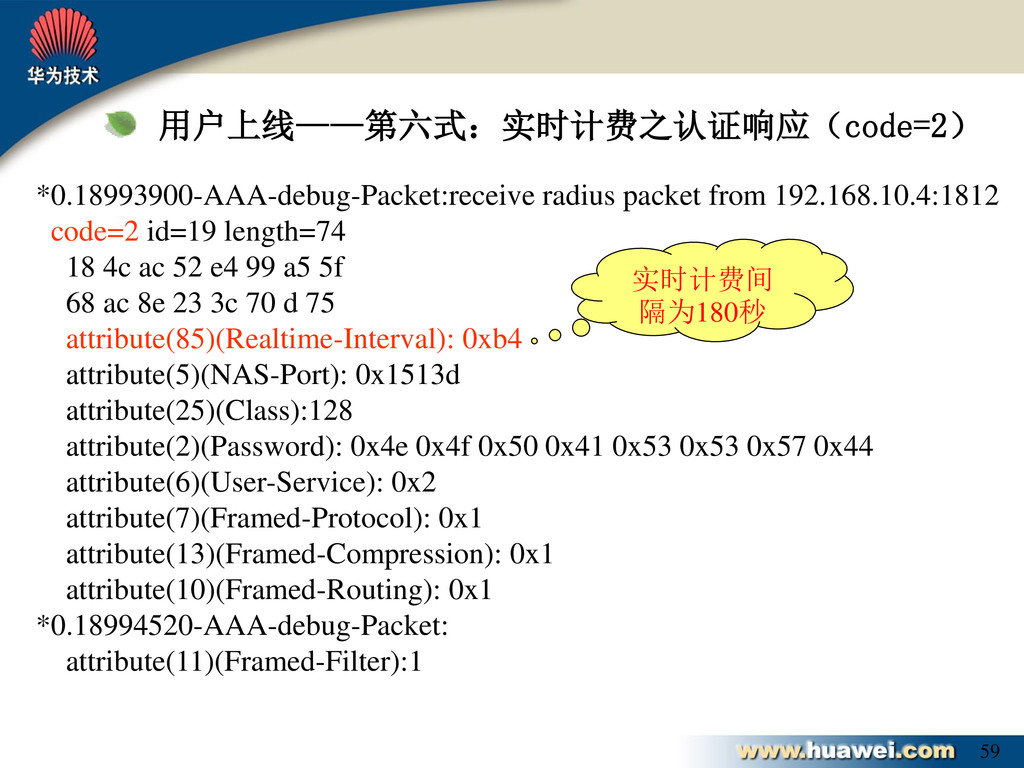
  30. 59 *0.18993900-AAA-debug-Packet:receive radius packet from 192.168.10.4:1812 code=2 id=19 length=74 18

    4c ac 52 e4 99 a5 5f 68 ac 8e 23 3c 70 d 75 attribute(85)(Realtime-Interval): 0xb4 attribute(5)(NAS-Port): 0x1513d attribute(25)(Class):128 attribute(2)(Password): 0x4e 0x4f 0x50 0x41 0x53 0x53 0x57 0x44 attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1 attribute(13)(Framed-Compression): 0x1 attribute(10)(Framed-Routing): 0x1 *0.18994520-AAA-debug-Packet: attribute(11)(Framed-Filter):1 用户上线——第六式:实时计费之认证响应(code=2) 实时计费间 隔为180秒
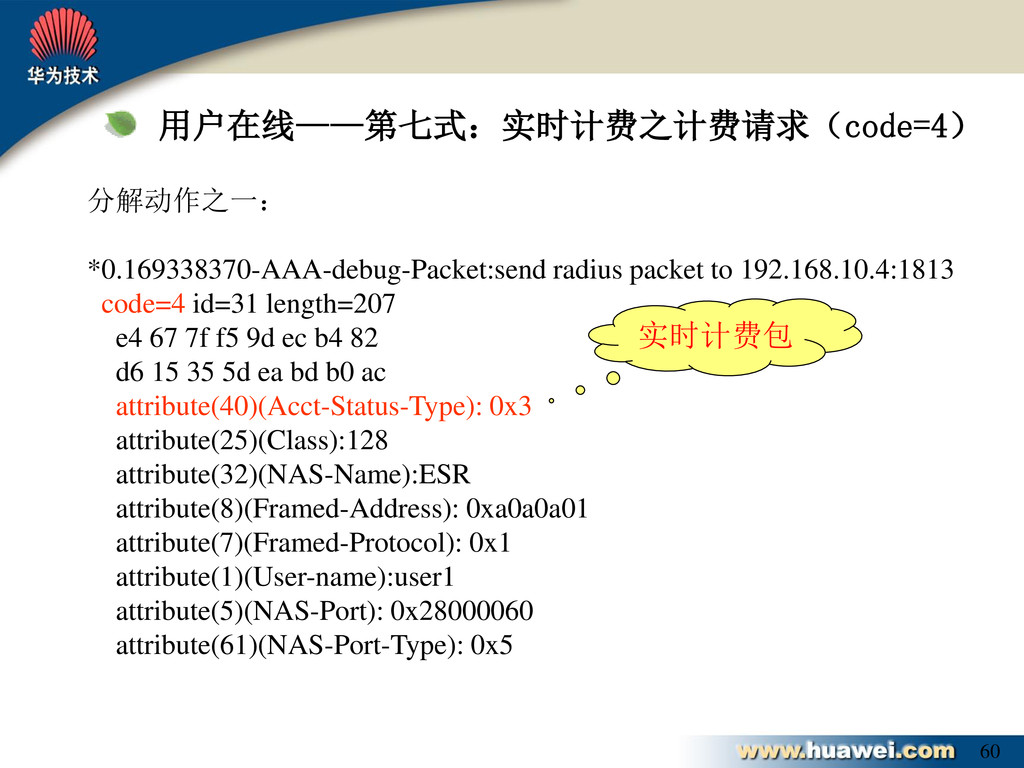
  31. 60 分解动作之一: *0.169338370-AAA-debug-Packet:send radius packet to 192.168.10.4:1813 code=4 id=31 length=207

    e4 67 7f f5 9d ec b4 82 d6 15 35 5d ea bd b0 ac attribute(40)(Acct-Status-Type): 0x3 attribute(25)(Class):128 attribute(32)(NAS-Name):ESR attribute(8)(Framed-Address): 0xa0a0a01 attribute(7)(Framed-Protocol): 0x1 attribute(1)(User-name):user1 attribute(5)(NAS-Port): 0x28000060 attribute(61)(NAS-Port-Type): 0x5 用户在线——第七式:实时计费之计费请求(code=4) 实时计费包
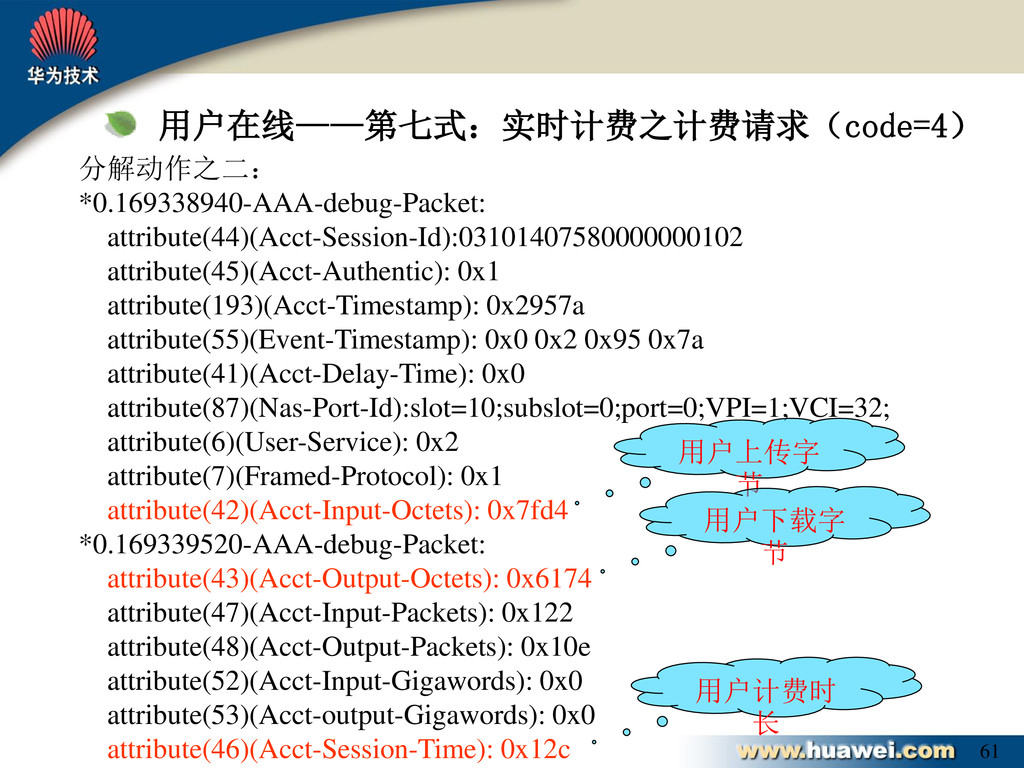
  32. 61 用户在线——第七式:实时计费之计费请求(code=4) 分解动作之二: *0.169338940-AAA-debug-Packet: attribute(44)(Acct-Session-Id):03101407580000000102 attribute(45)(Acct-Authentic): 0x1 attribute(193)(Acct-Timestamp): 0x2957a attribute(55)(Event-Timestamp):

    0x0 0x2 0x95 0x7a attribute(41)(Acct-Delay-Time): 0x0 attribute(87)(Nas-Port-Id):slot=10;subslot=0;port=0;VPI=1;VCI=32; attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1 attribute(42)(Acct-Input-Octets): 0x7fd4 *0.169339520-AAA-debug-Packet: attribute(43)(Acct-Output-Octets): 0x6174 attribute(47)(Acct-Input-Packets): 0x122 attribute(48)(Acct-Output-Packets): 0x10e attribute(52)(Acct-Input-Gigawords): 0x0 attribute(53)(Acct-output-Gigawords): 0x0 attribute(46)(Acct-Session-Time): 0x12c 用户上传字 节 用户下载字 节 用户计费时 长
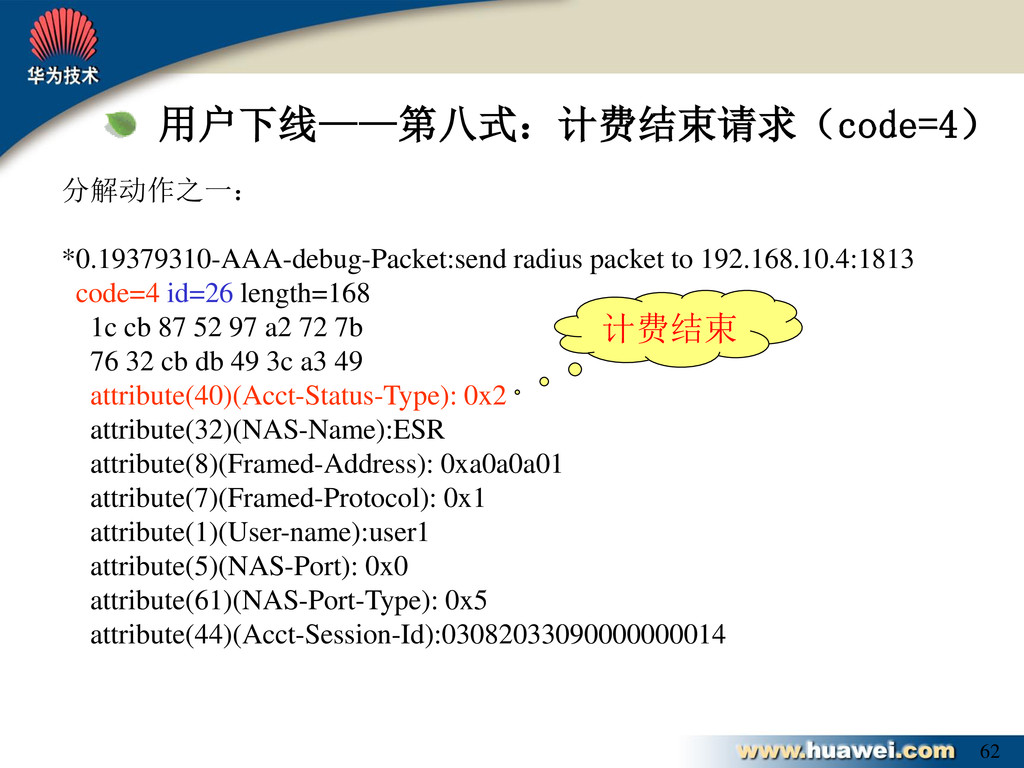
  33. 62 分解动作之一: *0.19379310-AAA-debug-Packet:send radius packet to 192.168.10.4:1813 code=4 id=26 length=168

    1c cb 87 52 97 a2 72 7b 76 32 cb db 49 3c a3 49 attribute(40)(Acct-Status-Type): 0x2 attribute(32)(NAS-Name):ESR attribute(8)(Framed-Address): 0xa0a0a01 attribute(7)(Framed-Protocol): 0x1 attribute(1)(User-name):user1 attribute(5)(NAS-Port): 0x0 attribute(61)(NAS-Port-Type): 0x5 attribute(44)(Acct-Session-Id):03082033090000000014 用户下线——第八式:计费结束请求(code=4) 计费结束
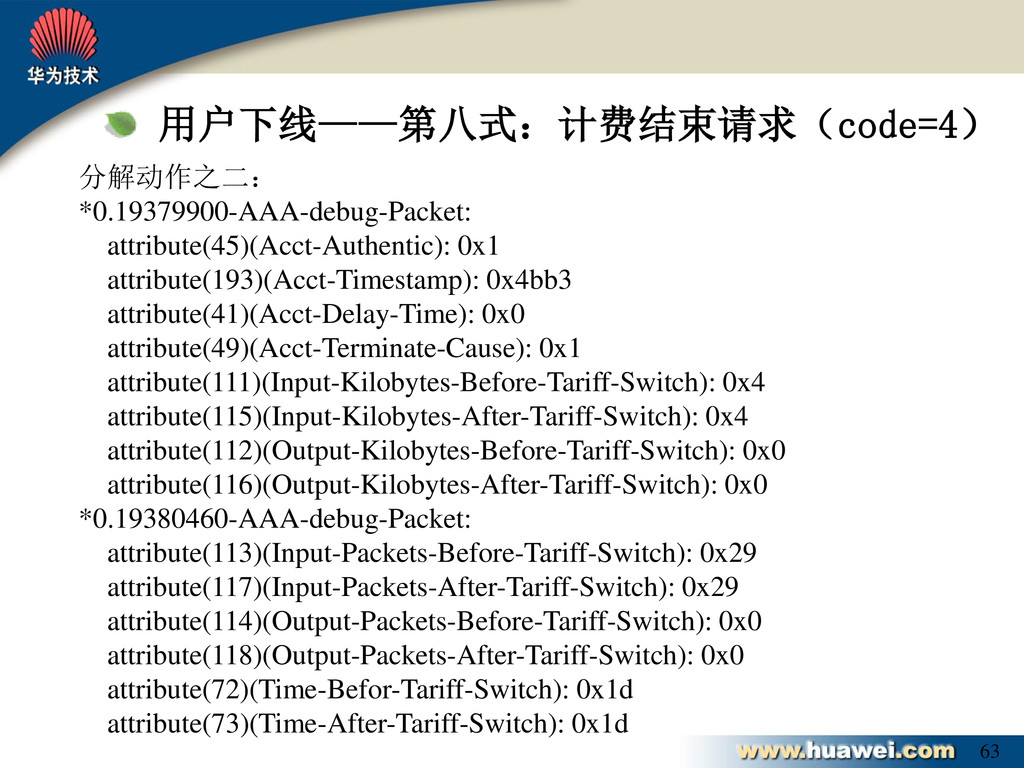
  34. 63 分解动作之二: *0.19379900-AAA-debug-Packet: attribute(45)(Acct-Authentic): 0x1 attribute(193)(Acct-Timestamp): 0x4bb3 attribute(41)(Acct-Delay-Time): 0x0 attribute(49)(Acct-Terminate-Cause):

    0x1 attribute(111)(Input-Kilobytes-Before-Tariff-Switch): 0x4 attribute(115)(Input-Kilobytes-After-Tariff-Switch): 0x4 attribute(112)(Output-Kilobytes-Before-Tariff-Switch): 0x0 attribute(116)(Output-Kilobytes-After-Tariff-Switch): 0x0 *0.19380460-AAA-debug-Packet: attribute(113)(Input-Packets-Before-Tariff-Switch): 0x29 attribute(117)(Input-Packets-After-Tariff-Switch): 0x29 attribute(114)(Output-Packets-Before-Tariff-Switch): 0x0 attribute(118)(Output-Packets-After-Tariff-Switch): 0x0 attribute(72)(Time-Befor-Tariff-Switch): 0x1d attribute(73)(Time-After-Tariff-Switch): 0x1d 用户下线——第八式:计费结束请求(code=4)
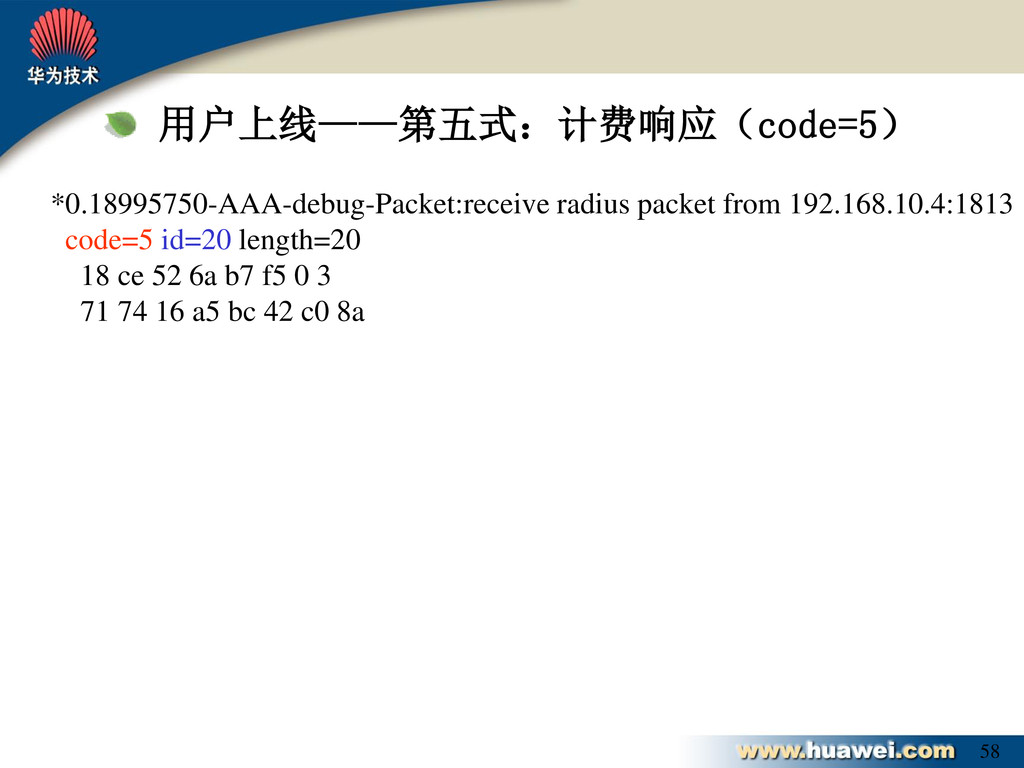
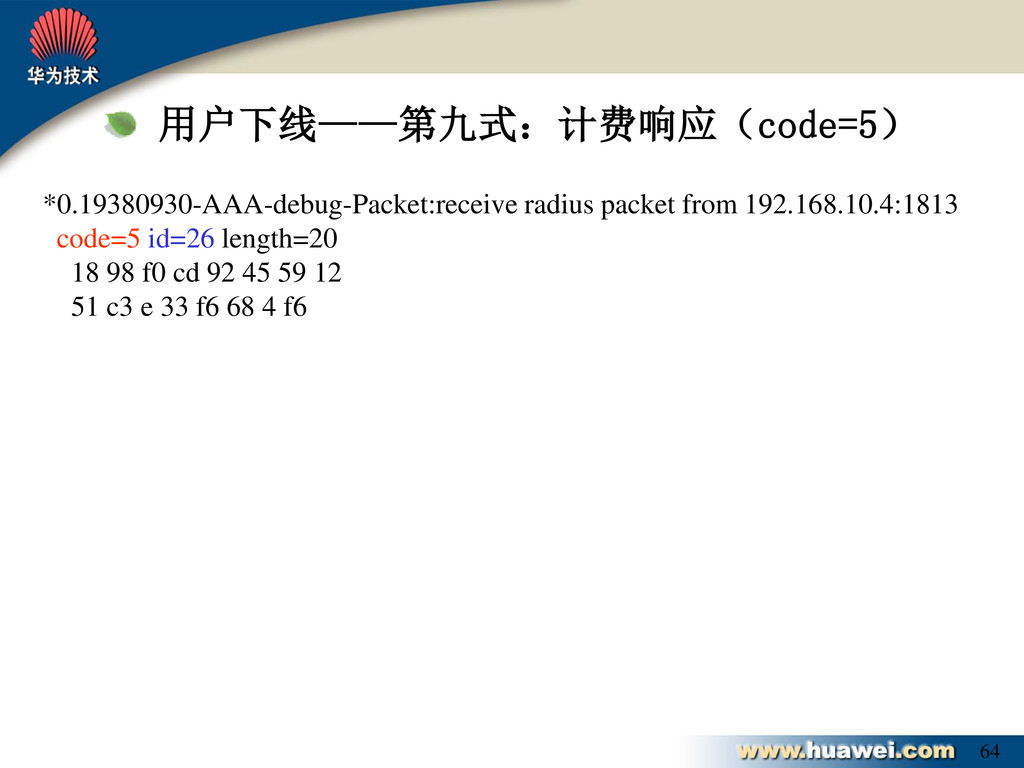
  35. 64 *0.19380930-AAA-debug-Packet:receive radius packet from 192.168.10.4:1813 code=5 id=26 length=20 18

    98 f0 cd 92 45 59 12 51 c3 e 33 f6 68 4 f6 用户下线——第九式:计费响应(code=5)
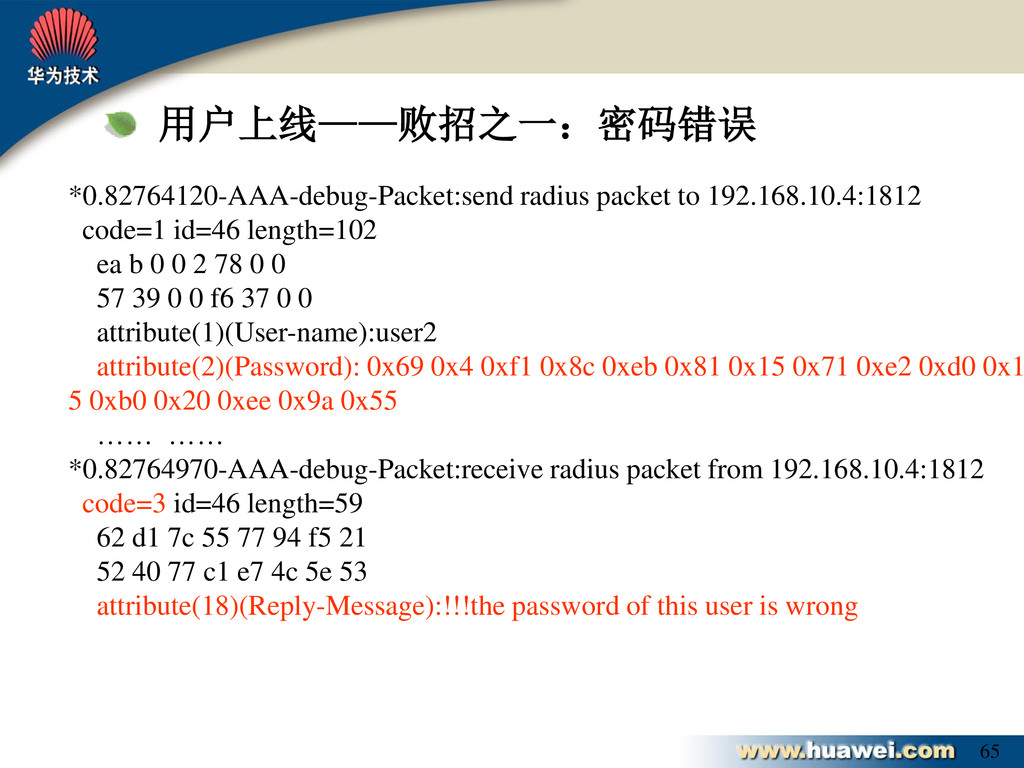
  36. 65 *0.82764120-AAA-debug-Packet:send radius packet to 192.168.10.4:1812 code=1 id=46 length=102 ea

    b 0 0 2 78 0 0 57 39 0 0 f6 37 0 0 attribute(1)(User-name):user2 attribute(2)(Password): 0x69 0x4 0xf1 0x8c 0xeb 0x81 0x15 0x71 0xe2 0xd0 0x1 5 0xb0 0x20 0xee 0x9a 0x55 …… …… *0.82764970-AAA-debug-Packet:receive radius packet from 192.168.10.4:1812 code=3 id=46 length=59 62 d1 7c 55 77 94 f5 21 52 40 77 c1 e7 4c 5e 53 attribute(18)(Reply-Message):!!!the password of this user is wrong 用户上线——败招之一:密码错误
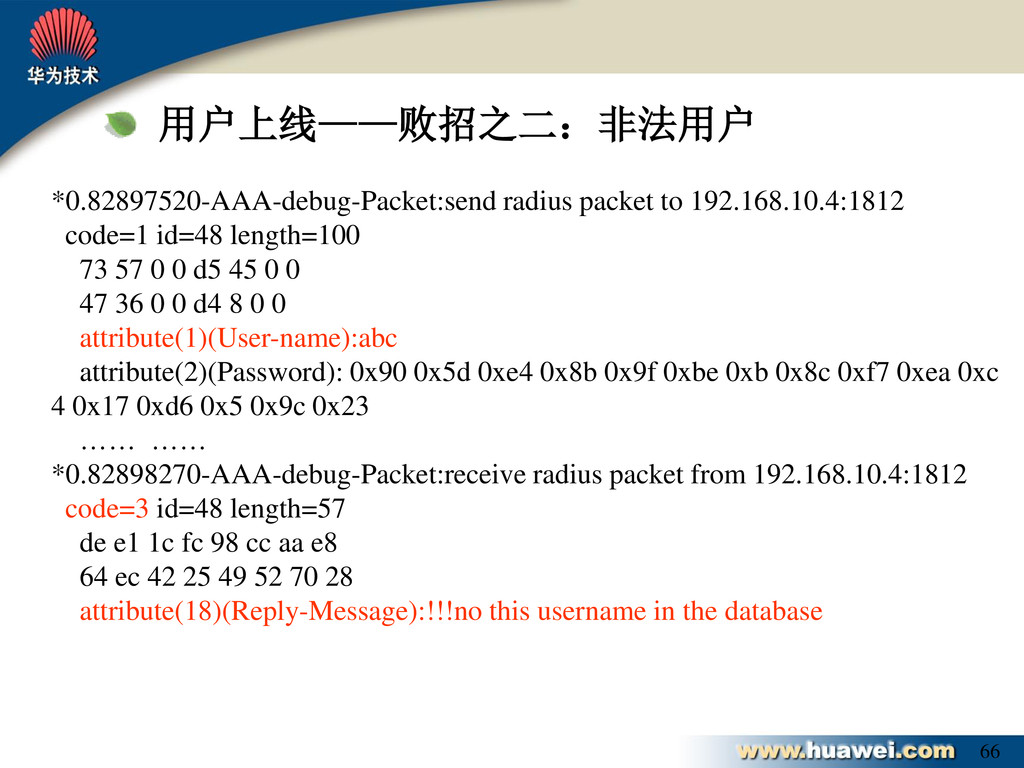
  37. 66 *0.82897520-AAA-debug-Packet:send radius packet to 192.168.10.4:1812 code=1 id=48 length=100 73

    57 0 0 d5 45 0 0 47 36 0 0 d4 8 0 0 attribute(1)(User-name):abc attribute(2)(Password): 0x90 0x5d 0xe4 0x8b 0x9f 0xbe 0xb 0x8c 0xf7 0xea 0xc 4 0x17 0xd6 0x5 0x9c 0x23 …… …… *0.82898270-AAA-debug-Packet:receive radius packet from 192.168.10.4:1812 code=3 id=48 length=57 de e1 1c fc 98 cc aa e8 64 ec 42 25 49 52 70 28 attribute(18)(Reply-Message):!!!no this username in the database 用户上线——败招之二:非法用户
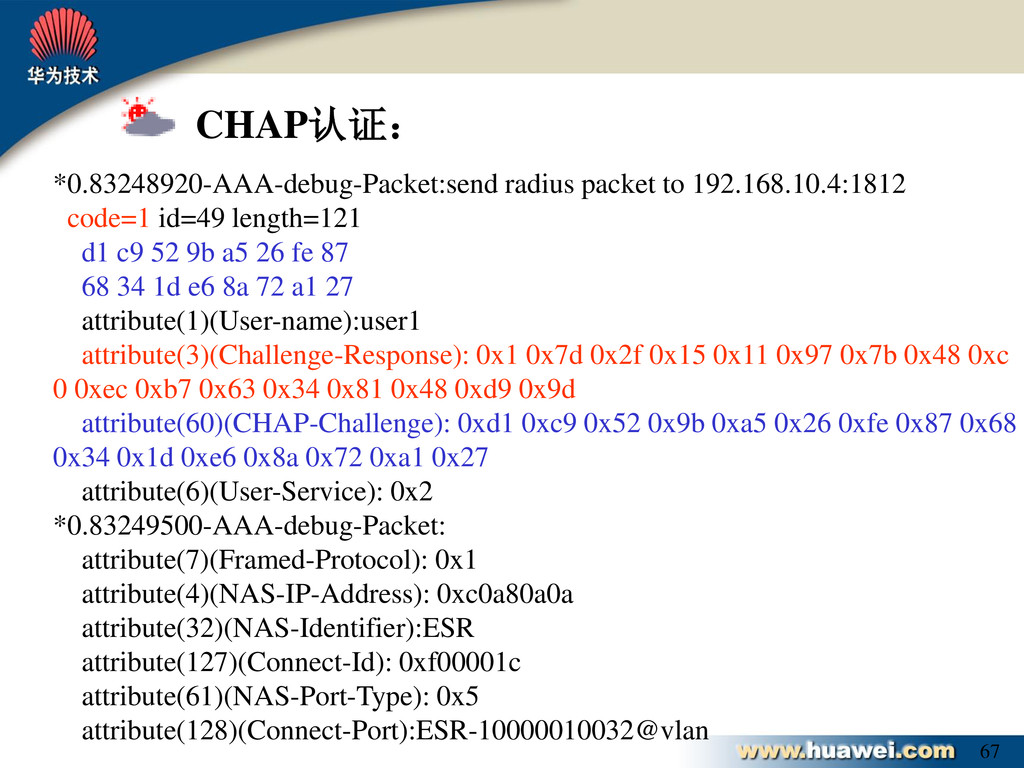
  38. 67 CHAP认证: *0.83248920-AAA-debug-Packet:send radius packet to 192.168.10.4:1812 code=1 id=49 length=121

    d1 c9 52 9b a5 26 fe 87 68 34 1d e6 8a 72 a1 27 attribute(1)(User-name):user1 attribute(3)(Challenge-Response): 0x1 0x7d 0x2f 0x15 0x11 0x97 0x7b 0x48 0xc 0 0xec 0xb7 0x63 0x34 0x81 0x48 0xd9 0x9d attribute(60)(CHAP-Challenge): 0xd1 0xc9 0x52 0x9b 0xa5 0x26 0xfe 0x87 0x68 0x34 0x1d 0xe6 0x8a 0x72 0xa1 0x27 attribute(6)(User-Service): 0x2 *0.83249500-AAA-debug-Packet: attribute(7)(Framed-Protocol): 0x1 attribute(4)(NAS-IP-Address): 0xc0a80a0a attribute(32)(NAS-Identifier):ESR attribute(127)(Connect-Id): 0xf00001c attribute(61)(NAS-Port-Type): 0x5 attribute(128)(Connect-Port):ESR-10000010032@vlan
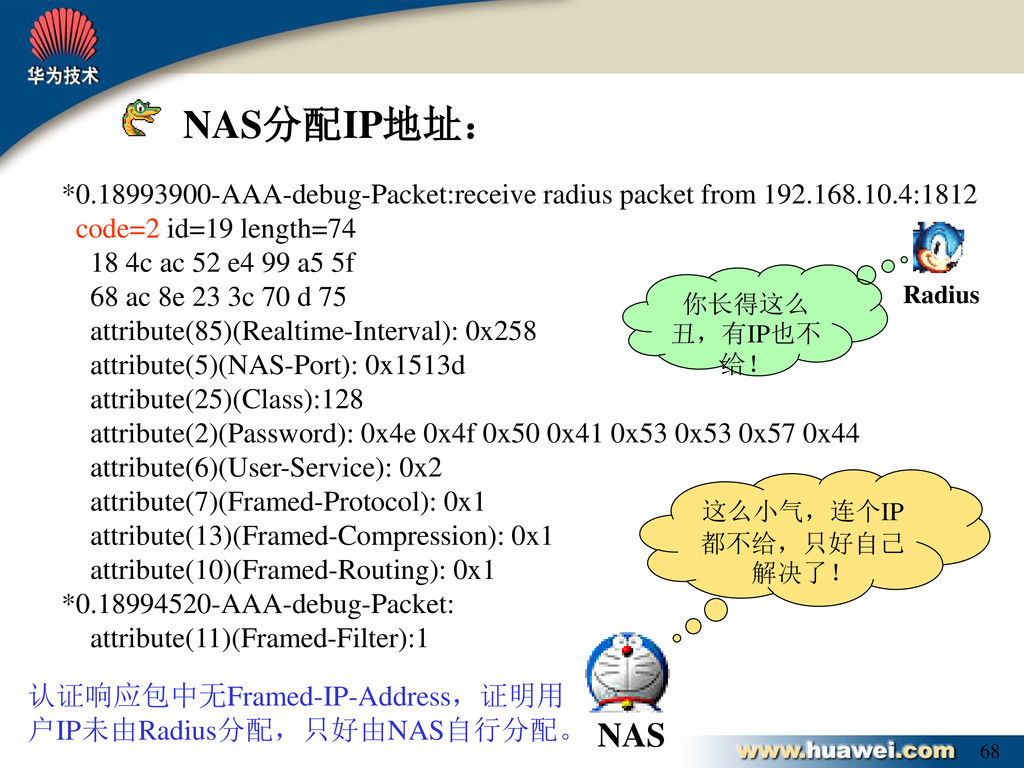
  39. 68 NAS分配IP地址: *0.18993900-AAA-debug-Packet:receive radius packet from 192.168.10.4:1812 code=2 id=19 length=74

    18 4c ac 52 e4 99 a5 5f 68 ac 8e 23 3c 70 d 75 attribute(85)(Realtime-Interval): 0x258 attribute(5)(NAS-Port): 0x1513d attribute(25)(Class):128 attribute(2)(Password): 0x4e 0x4f 0x50 0x41 0x53 0x53 0x57 0x44 attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1 attribute(13)(Framed-Compression): 0x1 attribute(10)(Framed-Routing): 0x1 *0.18994520-AAA-debug-Packet: attribute(11)(Framed-Filter):1 认证响应包中无Framed-IP-Address,证明用 户IP未由Radius分配,只好由NAS自行分配。 这么小气,连个IP 都不给,只好自己 解决了! NAS 你长得这么 丑,有IP也不 给! Radius
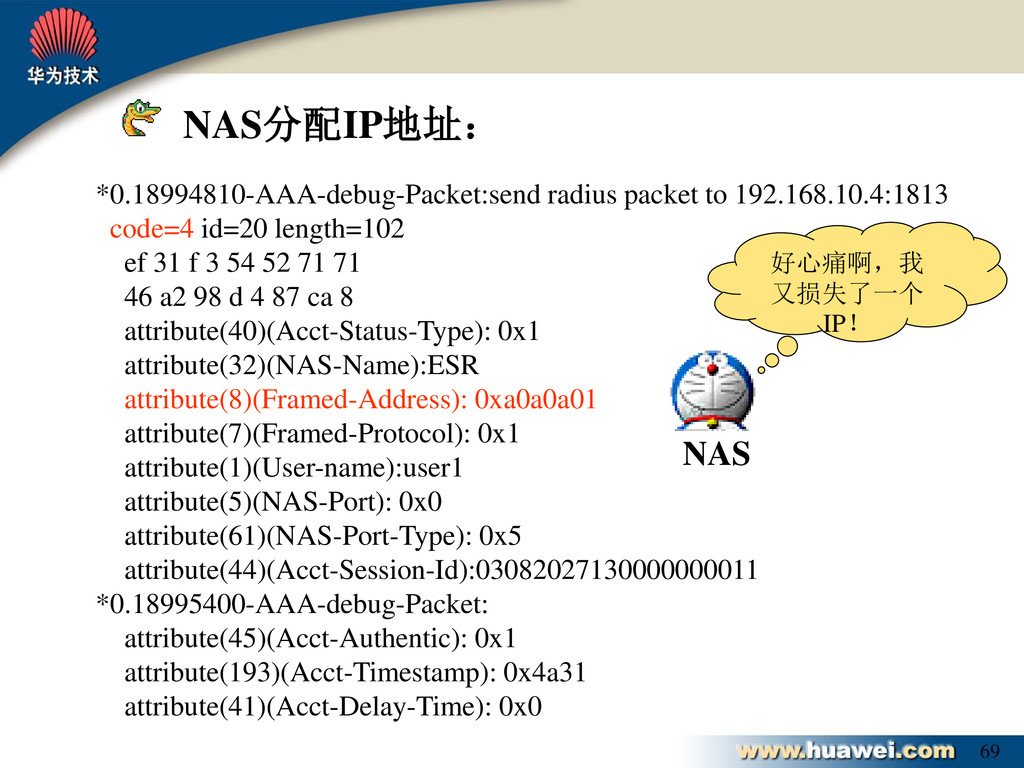
  40. 69 NAS分配IP地址: *0.18994810-AAA-debug-Packet:send radius packet to 192.168.10.4:1813 code=4 id=20 length=102

    ef 31 f 3 54 52 71 71 46 a2 98 d 4 87 ca 8 attribute(40)(Acct-Status-Type): 0x1 attribute(32)(NAS-Name):ESR attribute(8)(Framed-Address): 0xa0a0a01 attribute(7)(Framed-Protocol): 0x1 attribute(1)(User-name):user1 attribute(5)(NAS-Port): 0x0 attribute(61)(NAS-Port-Type): 0x5 attribute(44)(Acct-Session-Id):03082027130000000011 *0.18995400-AAA-debug-Packet: attribute(45)(Acct-Authentic): 0x1 attribute(193)(Acct-Timestamp): 0x4a31 attribute(41)(Acct-Delay-Time): 0x0 好心痛啊,我 又损失了一个 IP! NAS
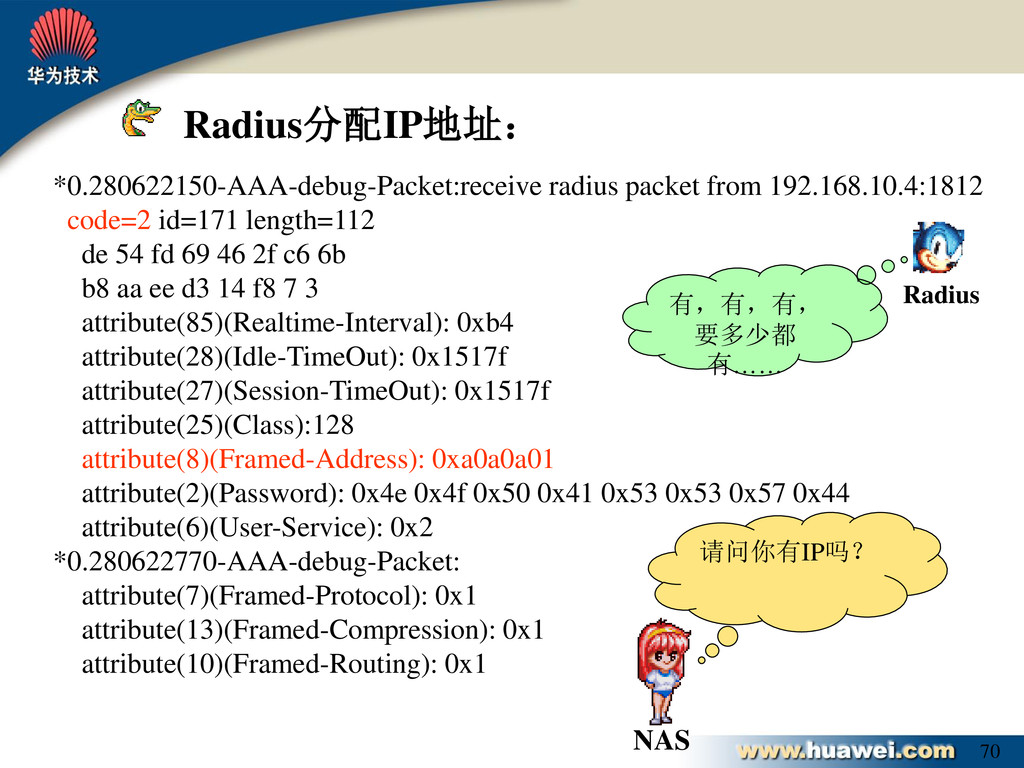
  41. 70 Radius分配IP地址: *0.280622150-AAA-debug-Packet:receive radius packet from 192.168.10.4:1812 code=2 id=171 length=112

    de 54 fd 69 46 2f c6 6b b8 aa ee d3 14 f8 7 3 attribute(85)(Realtime-Interval): 0xb4 attribute(28)(Idle-TimeOut): 0x1517f attribute(27)(Session-TimeOut): 0x1517f attribute(25)(Class):128 attribute(8)(Framed-Address): 0xa0a0a01 attribute(2)(Password): 0x4e 0x4f 0x50 0x41 0x53 0x53 0x57 0x44 attribute(6)(User-Service): 0x2 *0.280622770-AAA-debug-Packet: attribute(7)(Framed-Protocol): 0x1 attribute(13)(Framed-Compression): 0x1 attribute(10)(Framed-Routing): 0x1 有,有,有, 要多少都 有…… Radius 请问你有IP吗? NAS
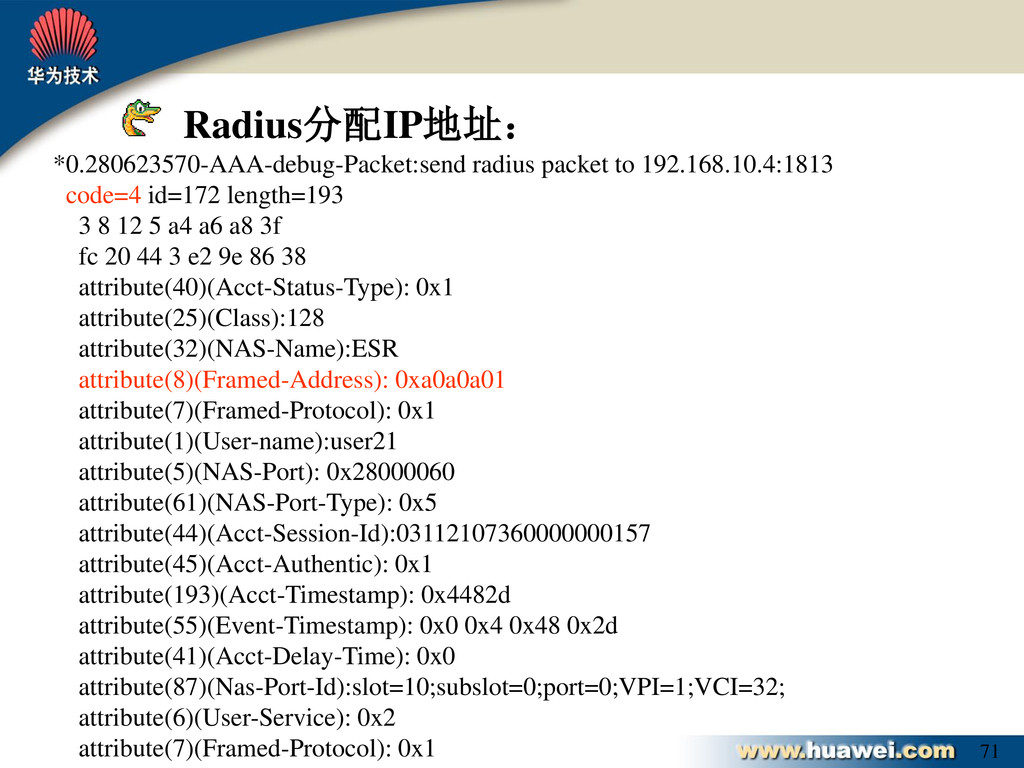
  42. 71 Radius分配IP地址: *0.280623570-AAA-debug-Packet:send radius packet to 192.168.10.4:1813 code=4 id=172 length=193

    3 8 12 5 a4 a6 a8 3f fc 20 44 3 e2 9e 86 38 attribute(40)(Acct-Status-Type): 0x1 attribute(25)(Class):128 attribute(32)(NAS-Name):ESR attribute(8)(Framed-Address): 0xa0a0a01 attribute(7)(Framed-Protocol): 0x1 attribute(1)(User-name):user21 attribute(5)(NAS-Port): 0x28000060 attribute(61)(NAS-Port-Type): 0x5 attribute(44)(Acct-Session-Id):03112107360000000157 attribute(45)(Acct-Authentic): 0x1 attribute(193)(Acct-Timestamp): 0x4482d attribute(55)(Event-Timestamp): 0x0 0x4 0x48 0x2d attribute(41)(Acct-Delay-Time): 0x0 attribute(87)(Nas-Port-Id):slot=10;subslot=0;port=0;VPI=1;VCI=32; attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1
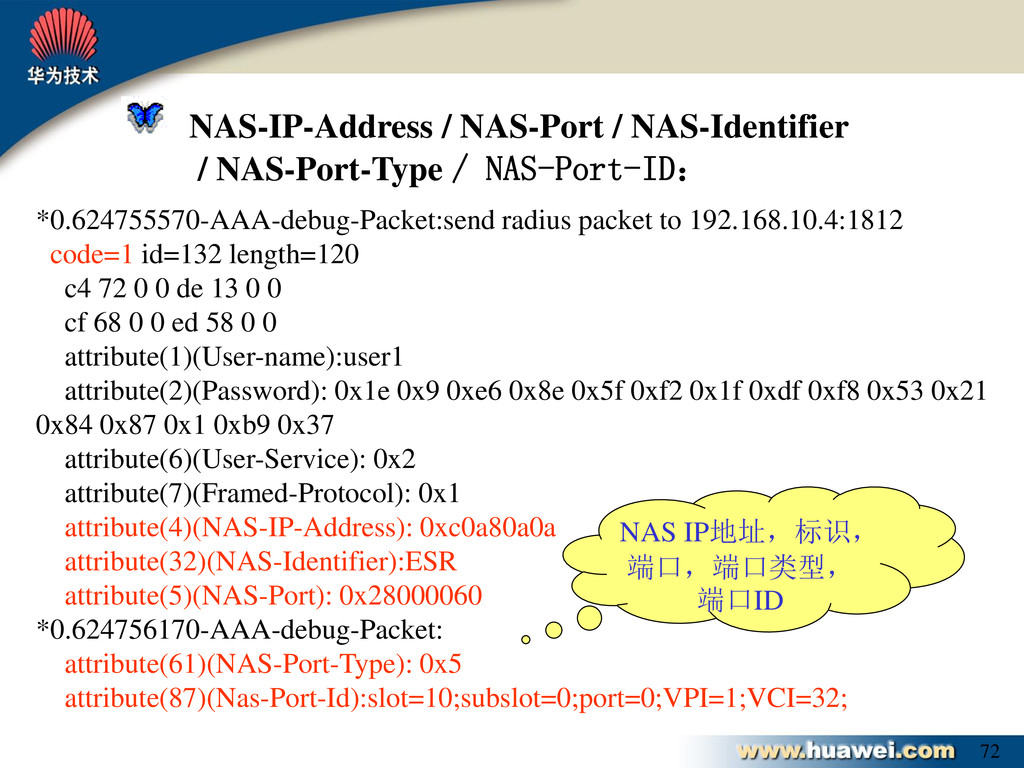
  43. 72 NAS-IP-Address / NAS-Port / NAS-Identifier / NAS-Port-Type / NAS-Port-ID:

    *0.624755570-AAA-debug-Packet:send radius packet to 192.168.10.4:1812 code=1 id=132 length=120 c4 72 0 0 de 13 0 0 cf 68 0 0 ed 58 0 0 attribute(1)(User-name):user1 attribute(2)(Password): 0x1e 0x9 0xe6 0x8e 0x5f 0xf2 0x1f 0xdf 0xf8 0x53 0x21 0x84 0x87 0x1 0xb9 0x37 attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1 attribute(4)(NAS-IP-Address): 0xc0a80a0a attribute(32)(NAS-Identifier):ESR attribute(5)(NAS-Port): 0x28000060 *0.624756170-AAA-debug-Packet: attribute(61)(NAS-Port-Type): 0x5 attribute(87)(Nas-Port-Id):slot=10;subslot=0;port=0;VPI=1;VCI=32; NAS IP地址,标识, 端口,端口类型, 端口ID
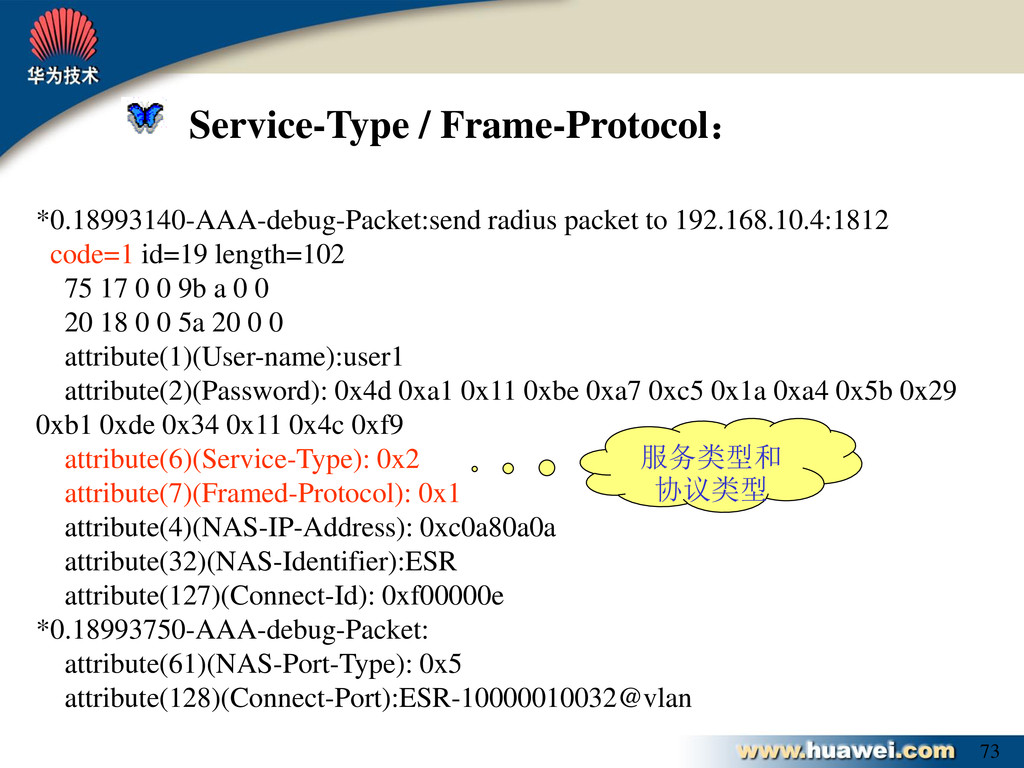
  44. 73 Service-Type / Frame-Protocol: *0.18993140-AAA-debug-Packet:send radius packet to 192.168.10.4:1812 code=1

    id=19 length=102 75 17 0 0 9b a 0 0 20 18 0 0 5a 20 0 0 attribute(1)(User-name):user1 attribute(2)(Password): 0x4d 0xa1 0x11 0xbe 0xa7 0xc5 0x1a 0xa4 0x5b 0x29 0xb1 0xde 0x34 0x11 0x4c 0xf9 attribute(6)(Service-Type): 0x2 attribute(7)(Framed-Protocol): 0x1 attribute(4)(NAS-IP-Address): 0xc0a80a0a attribute(32)(NAS-Identifier):ESR attribute(127)(Connect-Id): 0xf00000e *0.18993750-AAA-debug-Packet: attribute(61)(NAS-Port-Type): 0x5 attribute(128)(Connect-Port):ESR-10000010032@vlan 服务类型和 协议类型
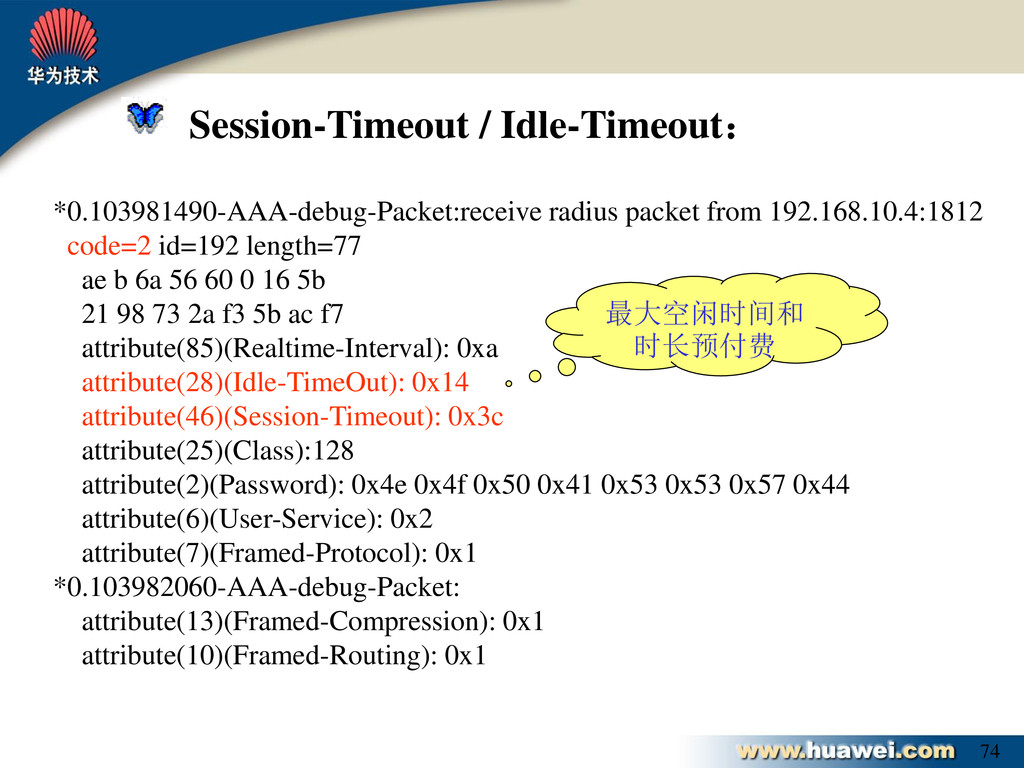
  45. 74 Session-Timeout / Idle-Timeout: *0.103981490-AAA-debug-Packet:receive radius packet from 192.168.10.4:1812 code=2

    id=192 length=77 ae b 6a 56 60 0 16 5b 21 98 73 2a f3 5b ac f7 attribute(85)(Realtime-Interval): 0xa attribute(28)(Idle-TimeOut): 0x14 attribute(46)(Session-Timeout): 0x3c attribute(25)(Class):128 attribute(2)(Password): 0x4e 0x4f 0x50 0x41 0x53 0x53 0x57 0x44 attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1 *0.103982060-AAA-debug-Packet: attribute(13)(Framed-Compression): 0x1 attribute(10)(Framed-Routing): 0x1 最大空闲时间和 时长预付费
  46. 75 …… …… …… attribute(44)(Acct-Session-Id):03101407580000000102 attribute(45)(Acct-Authentic): 0x1 attribute(193)(Acct-Timestamp): 0x2957a attribute(55)(Event-Timestamp):

    0x0 0x2 0x95 0x7a attribute(41)(Acct-Delay-Time): 0x0 attribute(87)(Nas-Port-Id):slot=10;subslot=0;port=0;VPI=1;VCI=32; attribute(6)(User-Service): 0x2 attribute(7)(Framed-Protocol): 0x1 attribute(42)(Acct-Input-Octets): 0x7fd4 *0.169339520-AAA-debug-Packet: attribute(43)(Acct-Output-Octets): 0x6174 attribute(47)(Acct-Input-Packets): 0x122 attribute(48)(Acct-Output-Packets): 0x10e attribute(52)(Acct-Input-Gigawords): 0x0 attribute(53)(Acct-output-Gigawords): 0x0 attribute(46)(Acct-Session-Time): 0x12c Acct-Session-ID / Acct-Authentic: 计费会话标识和 用户认证方式
  47. 76