Upgrade to Pro — share decks privately, control downloads, hide ads and more …

DevSecOps Bootcamp - Week 4 - Lesson 2

DevSecOps Bootcamp - Week 4 - Lesson 2

In this session, we'll figure out how to create and test alerts to detect security issues in our weakened app.

DevSecOps

June 17, 2016

Transcript

11 slides
  1. 1 BUILDING RUGGED SOFTWARE YEAR ONE / WEEK FOUR/ LESSON

    TWO Copyright © DevSecOps Foundation 2015-2016
  2. 2 Copyright © DevSecOps Foundation 2015-2016 • Field Extraction •

    Field Extraction with Regular Expressions • Statistics • Dashboards • Alerts Agenda
  3. 3 Copyright © DevSecOps Foundation 2015-2016 • Field Extraction •

    Key value pairs extracted by Splunk or by custom field extraction • Used by splunk to • Commands used to perform field extraction: rex, rename, stats, etc. Splunk Commands
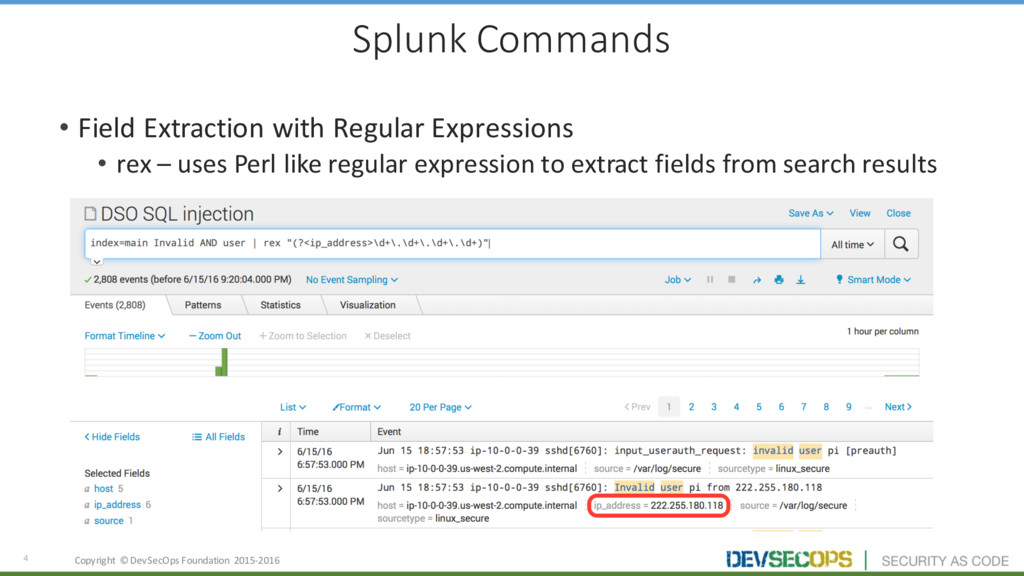
  4. 4 Copyright © DevSecOps Foundation 2015-2016 • Field Extraction with

    Regular Expressions • rex – uses Perl like regular expression to extract fields from search results Splunk Commands
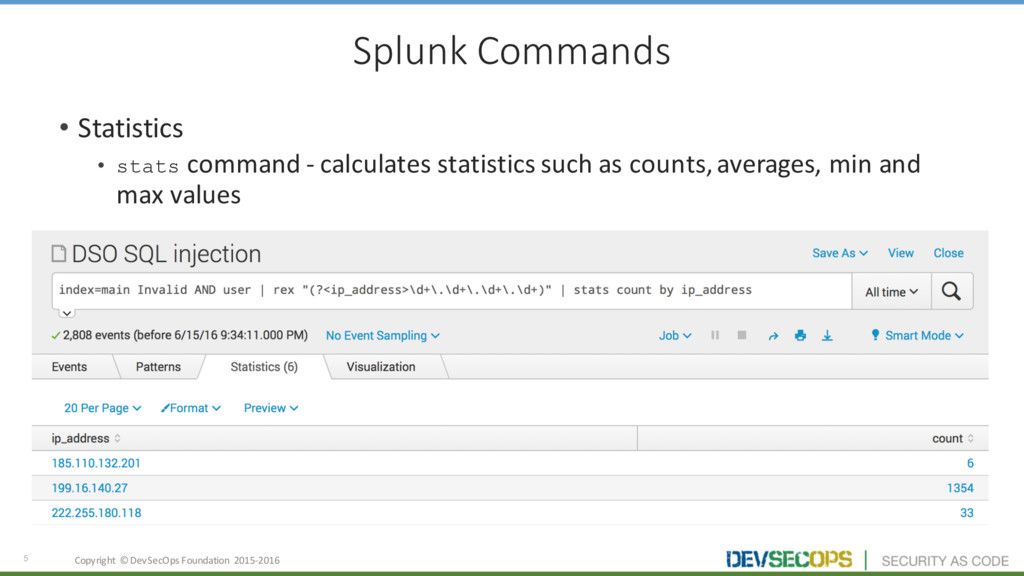
  5. 5 Copyright © DevSecOps Foundation 2015-2016 • Statistics • stats

    command - calculates statistics such as counts, averages, min and max values Splunk Commands
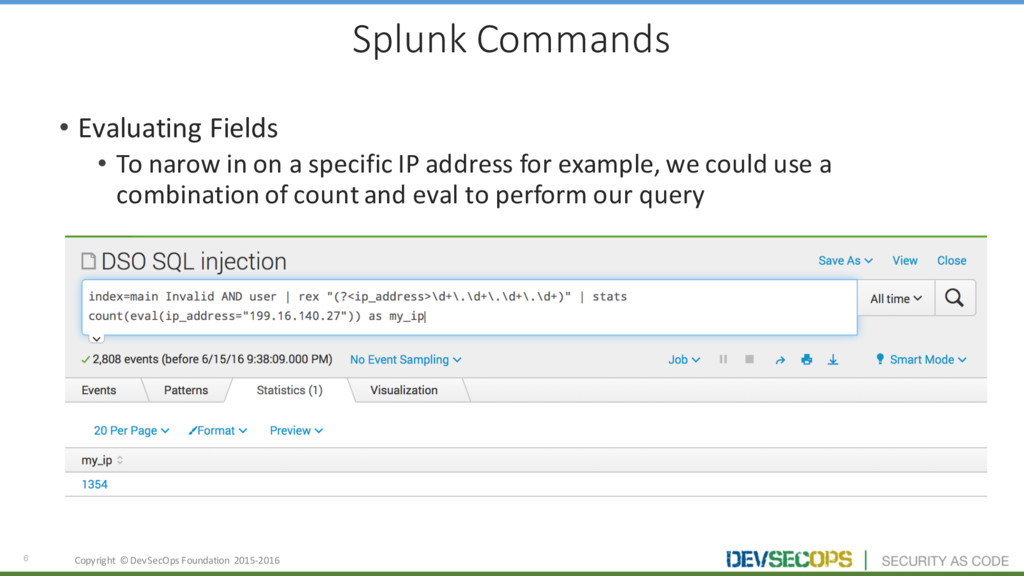
  6. 6 Copyright © DevSecOps Foundation 2015-2016 • Evaluating Fields •

    To narow in on a specific IP address for example, we could use a combination of count and eval to perform our query Splunk Commands
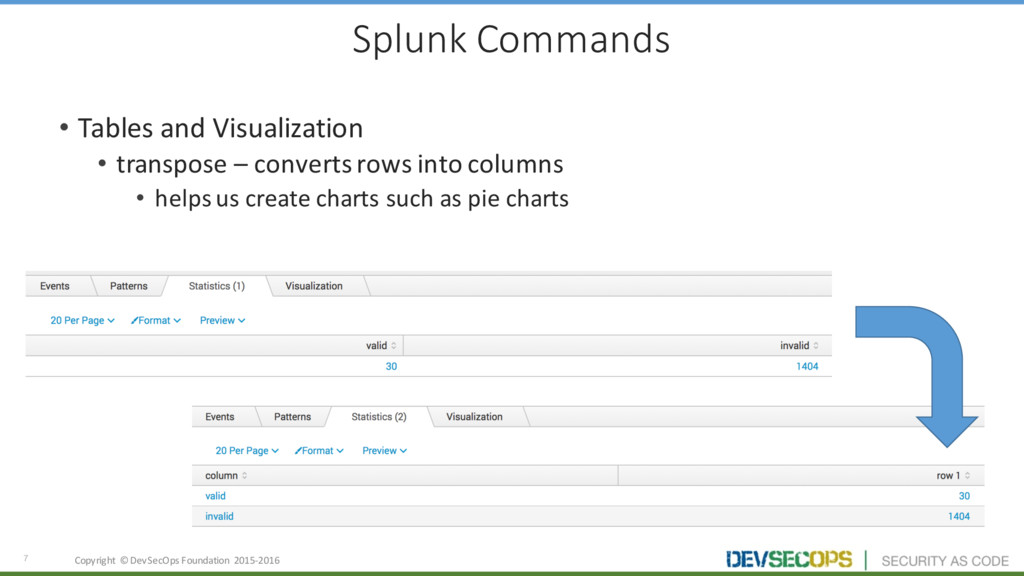
  7. 7 Copyright © DevSecOps Foundation 2015-2016 • Tables and Visualization

    • transpose – converts rows into columns • helps us create charts such as pie charts Splunk Commands
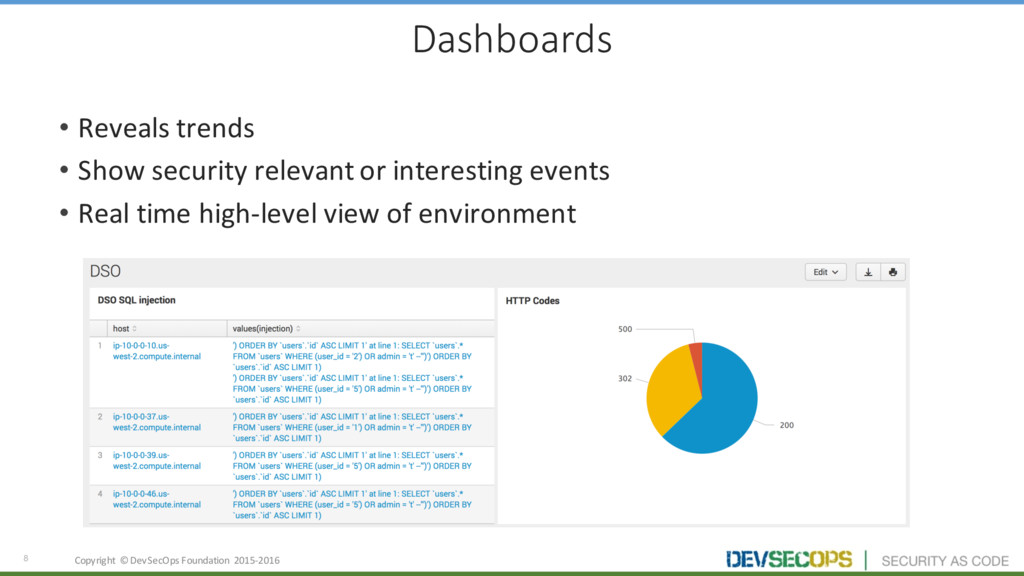
  8. 8 Copyright © DevSecOps Foundation 2015-2016 • Reveals trends •

    Show security relevant or interesting events • Real time high-level view of environment Dashboards
  9. 9 Copyright © DevSecOps Foundation 2015-2016 • Alerts can be

    used to • Drive a report • Send an email • Execute a Splunk app • Execute a custom script • Initiate incident response Alerts
  10. 11 Copyright © DevSecOps Foundation 2015-2016 • If you weren’t

    here last week team up with someone who was or quickly do week 3 lab 2 (get AWS credentials from Instructor) • If you were here last week: • Run through the exercises in week 3 lab 3 if Splunk searches return no data Lab 2

More Decks by DevSecOps

Other Decks in Technology