Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Deep Dive Into Threat Hunting

Sponsored · Ship Features Fearlessly Turn features on and off without deploys. Used by thousands of Ruby developers. →
Avatar for foxyproxy foxyproxy
October 24, 2021

Deep Dive Into Threat Hunting

Event: Know How Version 2.0 EP:01 [Rootec Stak]

Topic: Deep Dive Into Threat Hunting

Presented by : Harisuthan.S

Blog: https://www.socinvestigation.com/author/harisuthan/

Linked IN: https://www.linkedin.com/in/harisuthan-s-21365b17a/

Avatar for foxyproxy

foxyproxy

October 24, 2021

Other Decks in Technology

Transcript

  1. WHOA! Hari suthan.S Information Security Analyst @ FIS Global Cyber

    security aspirant | Exploring RED & BLUE Team stuffs https://www.socinvestigation.com/author/harisuthan/
  2. What is Threat Hunting Threat Hunting Loops 01 02 Challenges

    & Goal 03 04 TABLE OF CONTENTS CONCLUSION
  3. THE CYBER Defence A proactive or reactive approach to defend

    or protect the organisation assets from the external intruders. Simply to achieve CIA Confidentiality+Integrity+Availability
  4. What is Threat - Intention of harm - Generally threat

    is an term to inflict pain injure or damage, to be more specific to Cyber sec “A Malicious act that seeks to steal,disrupt or damage data” Many researchers believe threat hunting no longer an option but necessary
  5. Hunting VS Intelligence Intel Hunting Threat intelligence is the gathering

    of data on emerging or existing threat actors Proactive detection of malicious activity, simply a combination of
  6. Intelligence An strategy or an technique to identify or prioritize

    organization assets to prevent or mitigate cyber risks, hence assets include servers, workstations, etc, it generally depends on the organization’s postures. Ex : Crown Jewels Analysis
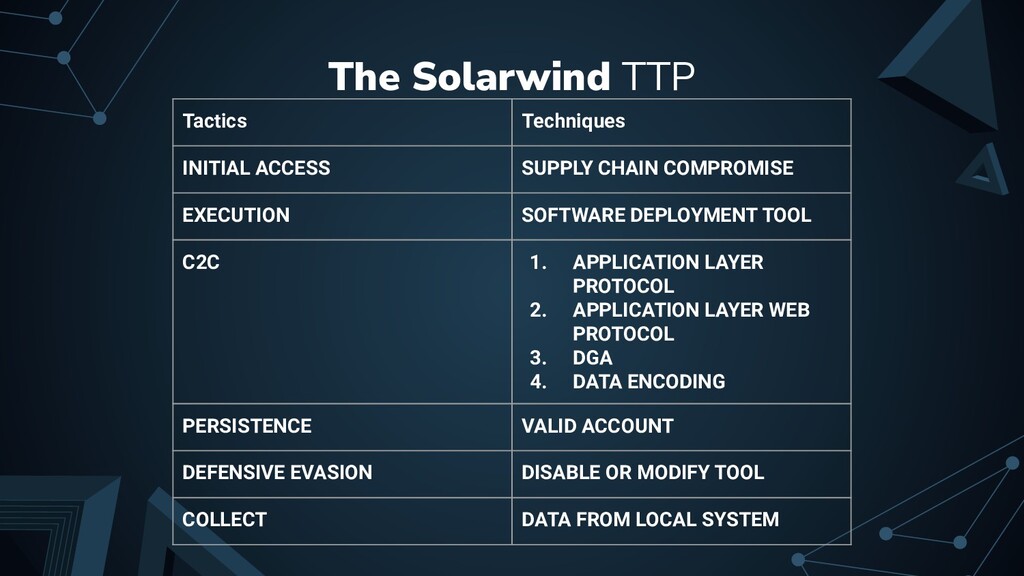
  7. The Solarwind TTP Tactics Techniques INITIAL ACCESS SUPPLY CHAIN COMPROMISE

    EXECUTION SOFTWARE DEPLOYMENT TOOL C2C 1. APPLICATION LAYER PROTOCOL 2. APPLICATION LAYER WEB PROTOCOL 3. DGA 4. DATA ENCODING PERSISTENCE VALID ACCOUNT DEFENSIVE EVASION DISABLE OR MODIFY TOOL COLLECT DATA FROM LOCAL SYSTEM
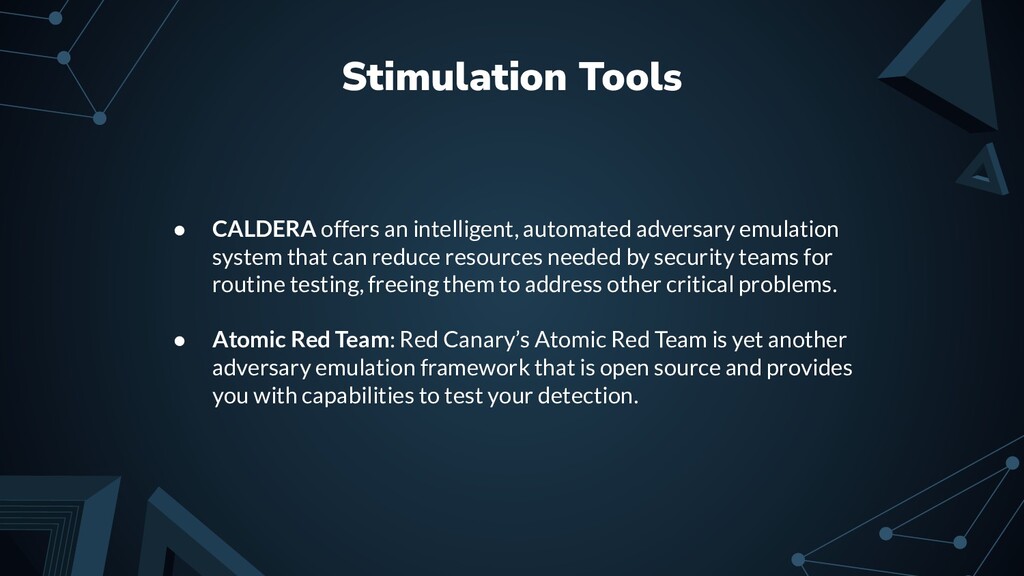
  8. Stimulation Tools • CALDERA offers an intelligent, automated adversary emulation

    system that can reduce resources needed by security teams for routine testing, freeing them to address other critical problems. • Atomic Red Team: Red Canary’s Atomic Red Team is yet another adversary emulation framework that is open source and provides you with capabilities to test your detection.
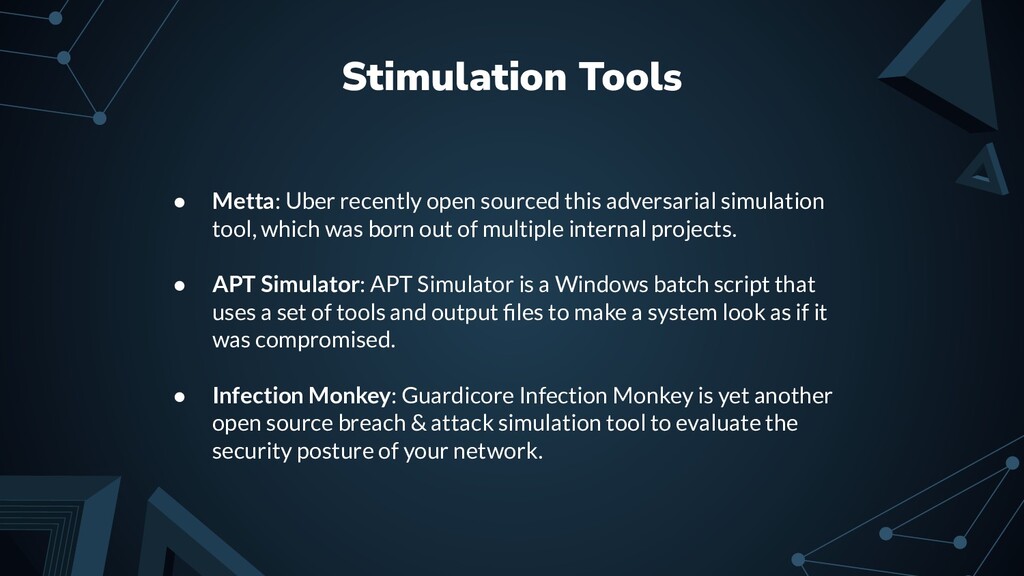
  9. Stimulation Tools • Metta: Uber recently open sourced this adversarial

    simulation tool, which was born out of multiple internal projects. • APT Simulator: APT Simulator is a Windows batch script that uses a set of tools and output files to make a system look as if it was compromised. • Infection Monkey: Guardicore Infection Monkey is yet another open source breach & attack simulation tool to evaluate the security posture of your network.
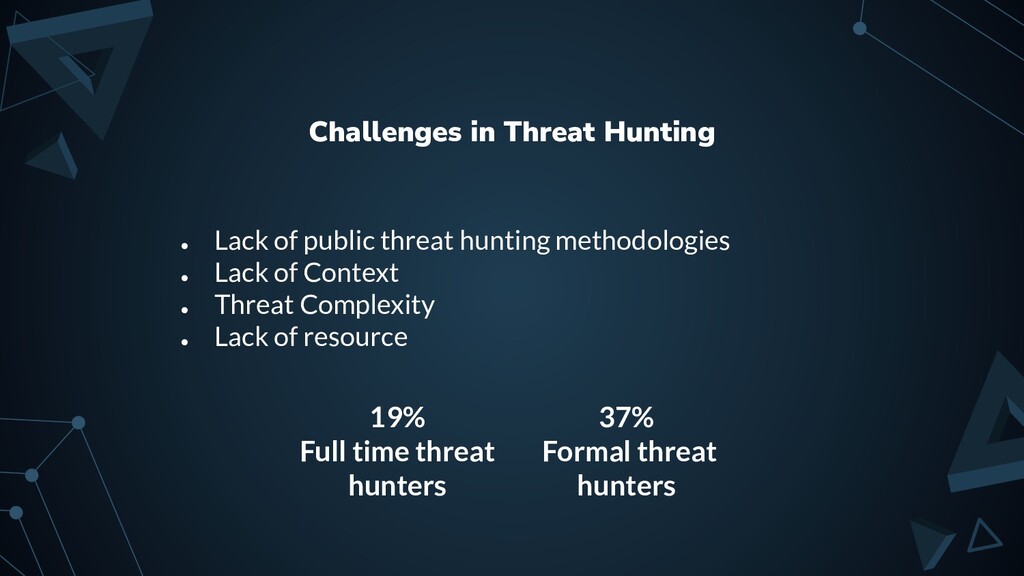
  10. Challenges in Threat Hunting • Lack of public threat hunting

    methodologies • Lack of Context • Threat Complexity • Lack of resource 19% Full time threat hunters 37% Formal threat hunters
  11. Goals • Minimize residual risk • Detect advanced attack •

    TTP based detection • Behavior based analysis
  12. Conclusion • “A Malicious act that seeks to steal,disrupt or

    damage data” • Many researchers believe threat hunting no longer an option but necessary • A formal threat hunting model providing a focused approach