Share
Embed
Funky Malware Formats
Presented at SAS 2019: https://sas.kaspersky.com/#wednesday-april-10-2019-conference-day-2-sas
Video #1: https://www.youtube.com/watch?v=0ndK-Az0RO4
Video #2 (extended version): https://www.youtube.com/watch?v=fvKeV5oJMnc
Additional materials: https://github.com/hasherezade/funky_malware_formats
hasherezade
April 10, 2019
Transcript
74 slides
-
INTRODUCTION What is this talk about? • Custom PE loaders
are typical in malware nowadays • How common are custom formats? • We set out to answer this very question • Much like searching for new forms of life • We bring you some of our findings in this talk • But before so… -
ABOUT US Meet the special agents Mark Lechtik Aleksandra Doniec
@_marklech_ Check Point Research @hasherezade Malwarebytes -
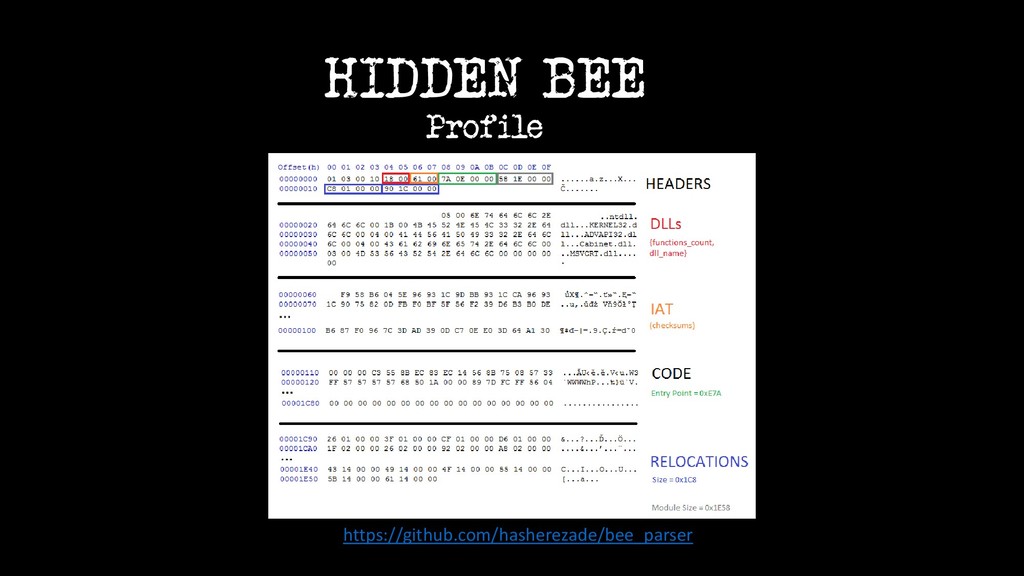
• Distributed by Underminer EK • Chinese miner • High
and low-level elements: including a bootkit • We will focus on the high-level part: loaders in custom format HIDDEN BEE Profile -
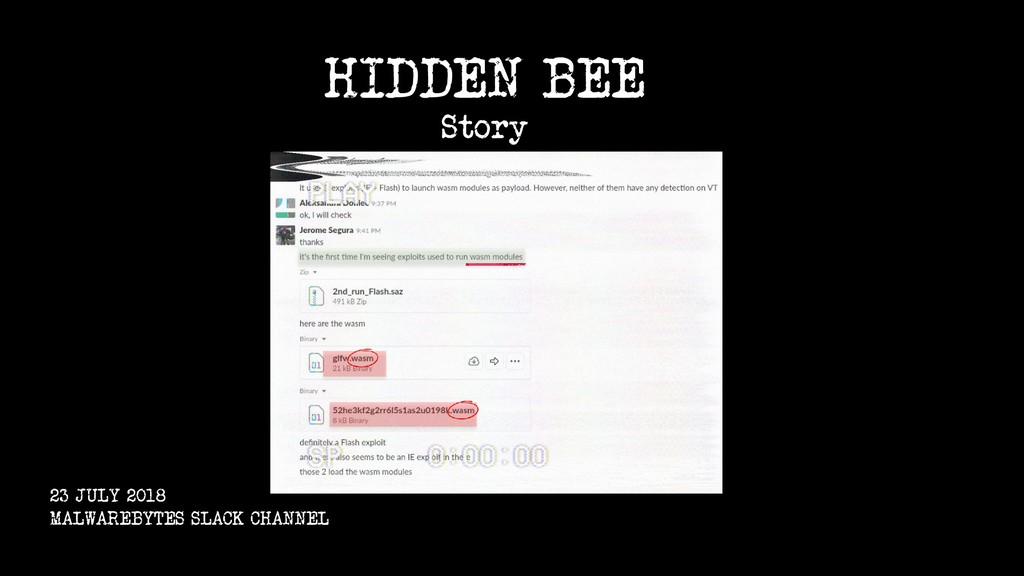
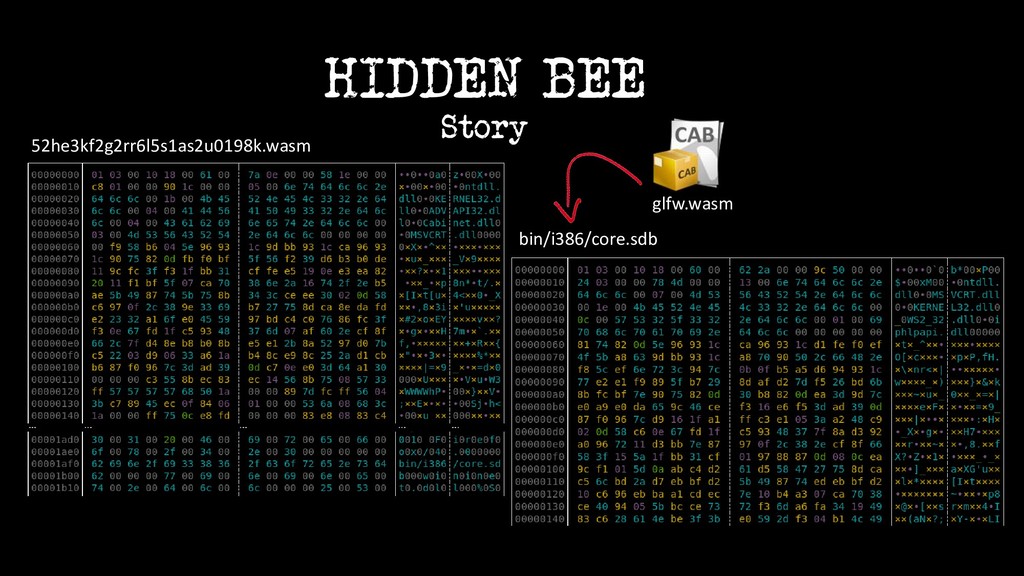
? This is not how the WASM file looks like...
? HIDDEN BEE Story -
• We don’t have: the initial loader • We have:
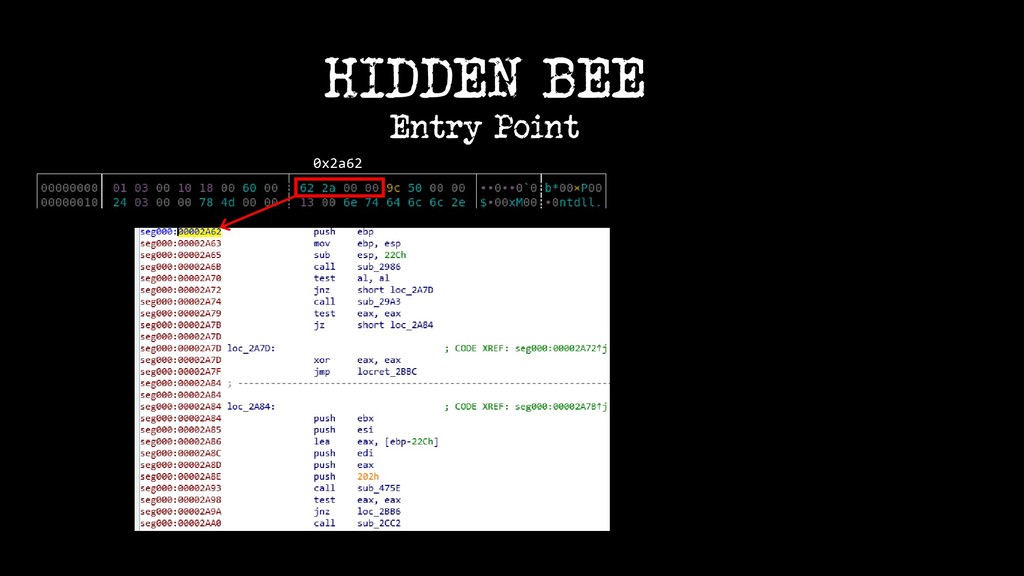
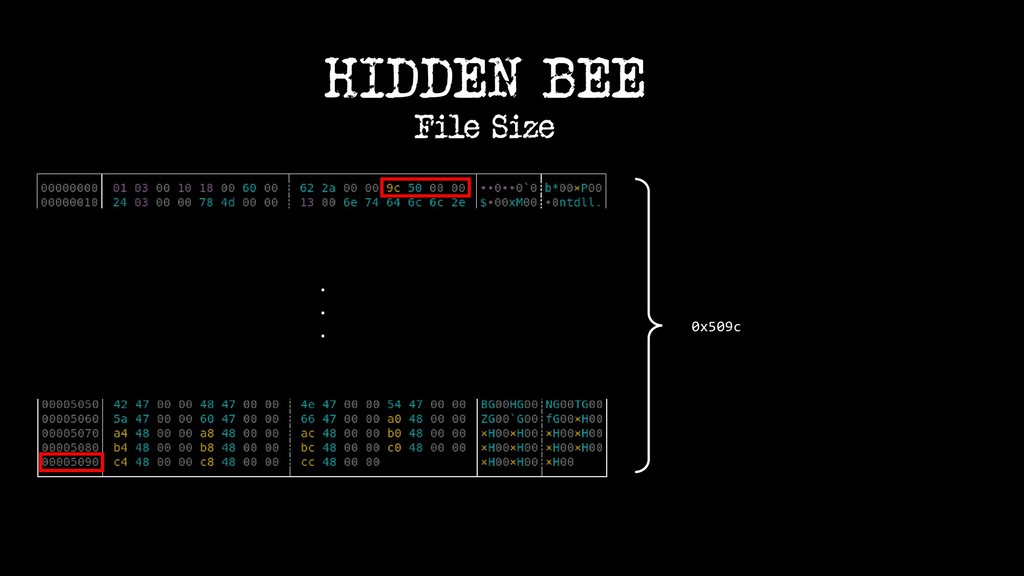
2 files with a consistent format • Let’s try to analyze the headers and guess what each field means • Let’s write our own loader HIDDEN BEE Story -
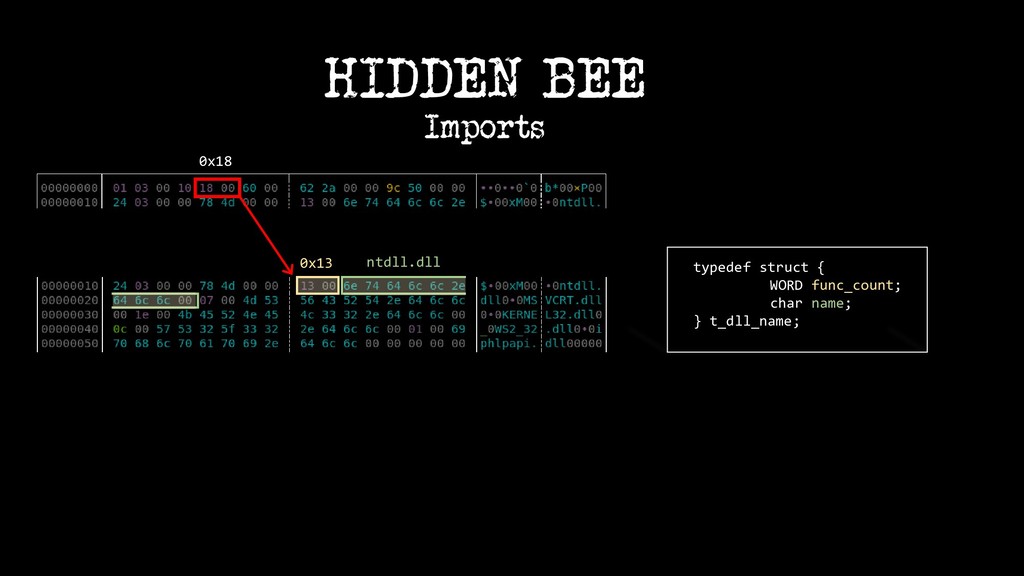
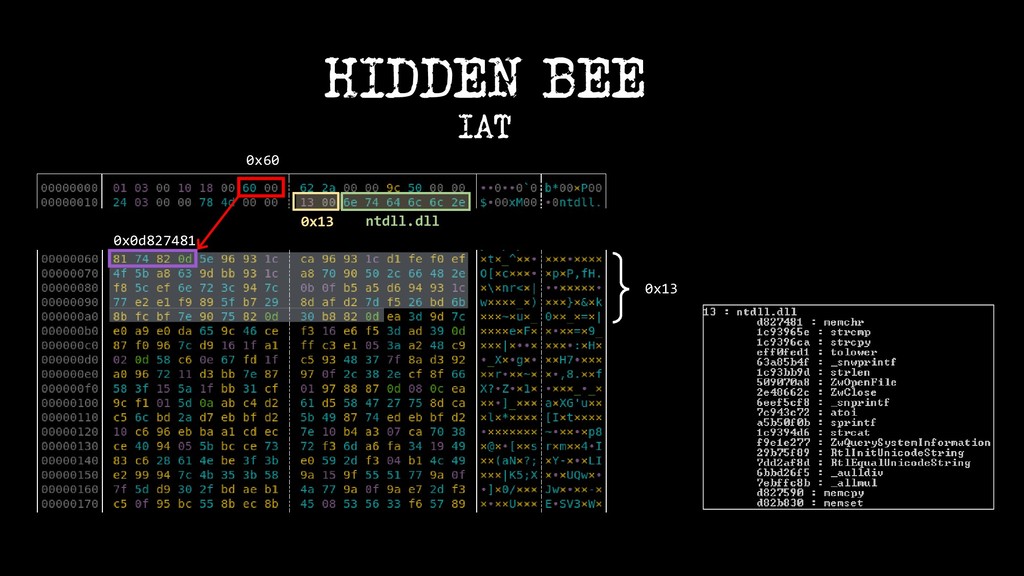
typedef struct { WORD func_count; char name; } t_dll_name; ntdll.dll
HIDDEN BEE Imports 0x13 0x18 -
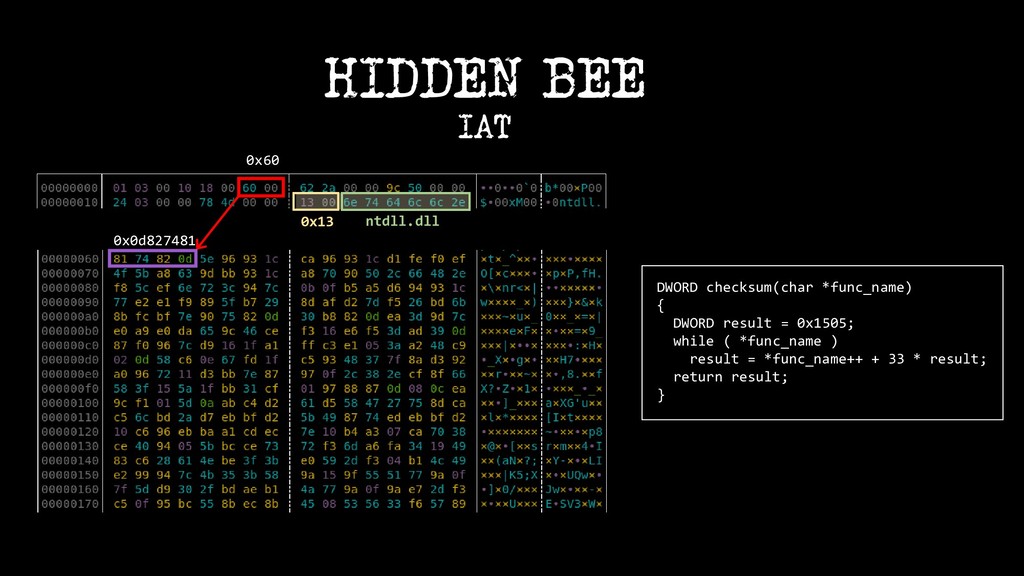
DWORD checksum(char *func_name) { DWORD result = 0x1505; while (
*func_name ) result = *func_name++ + 33 * result; return result; } 0x60 0x0d827481 ntdll.dll HIDDEN BEE IAT 0x13 -
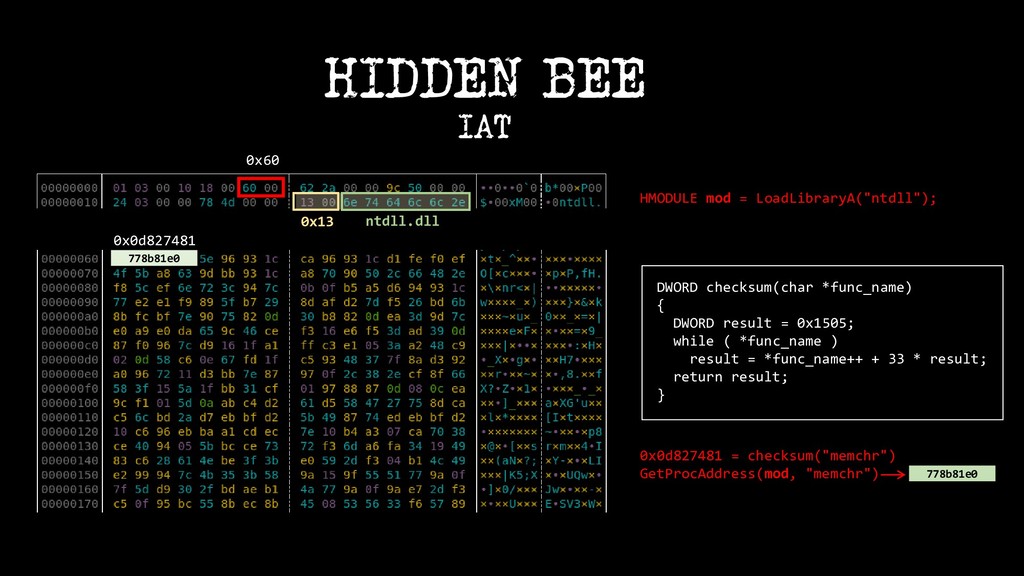
DWORD checksum(char *func_name) { DWORD result = 0x1505; while (
*func_name ) result = *func_name++ + 33 * result; return result; } 0x0d827481 778b81e0 0x0d827481 = checksum("memchr") GetProcAddress(mod, "memchr") 778b81e0 HMODULE mod = LoadLibraryA("ntdll"); HIDDEN BEE IAT 0x60 ntdll.dll 0x13 -
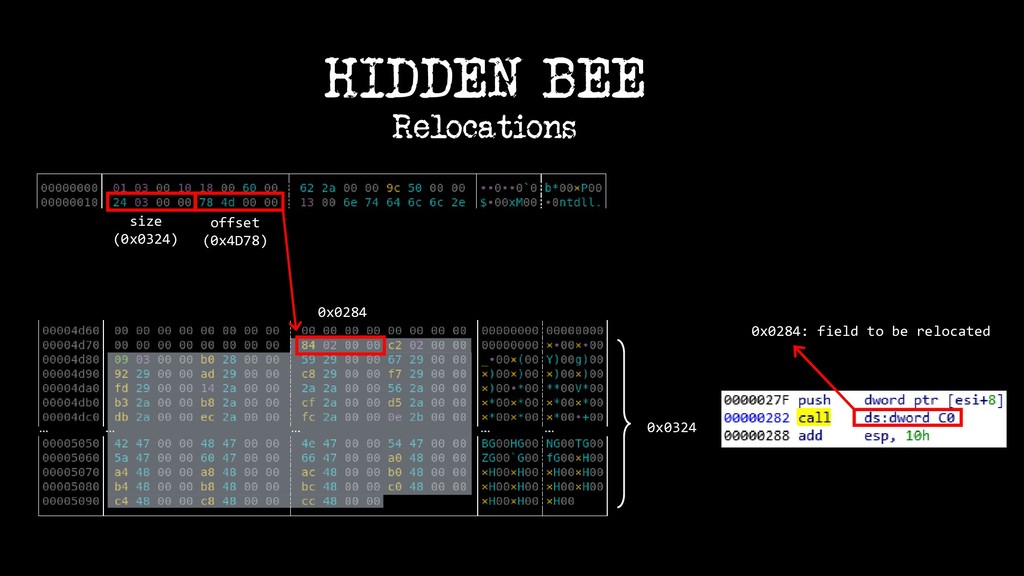
offset (0x4D78) size (0x0324) 0x0324 0x0284 HIDDEN BEE Relocations 0x0284:
field to be relocated -
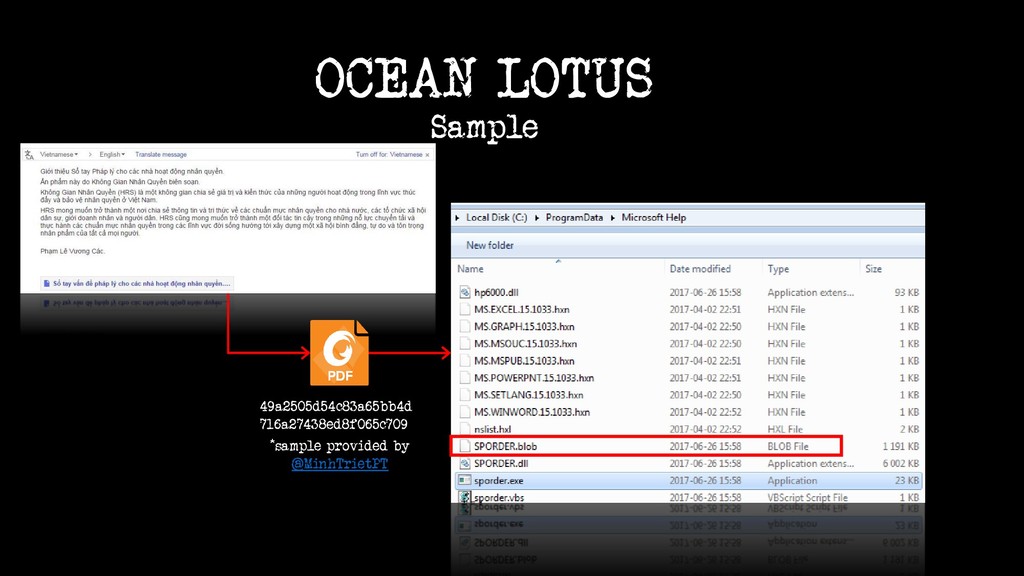
• Known as a Vietnamese APT32 group • Distributed mainly
by phishing and waterholing attacks • Payloads of various types, often composed of multiple files OCEAN LOTUS Profile -
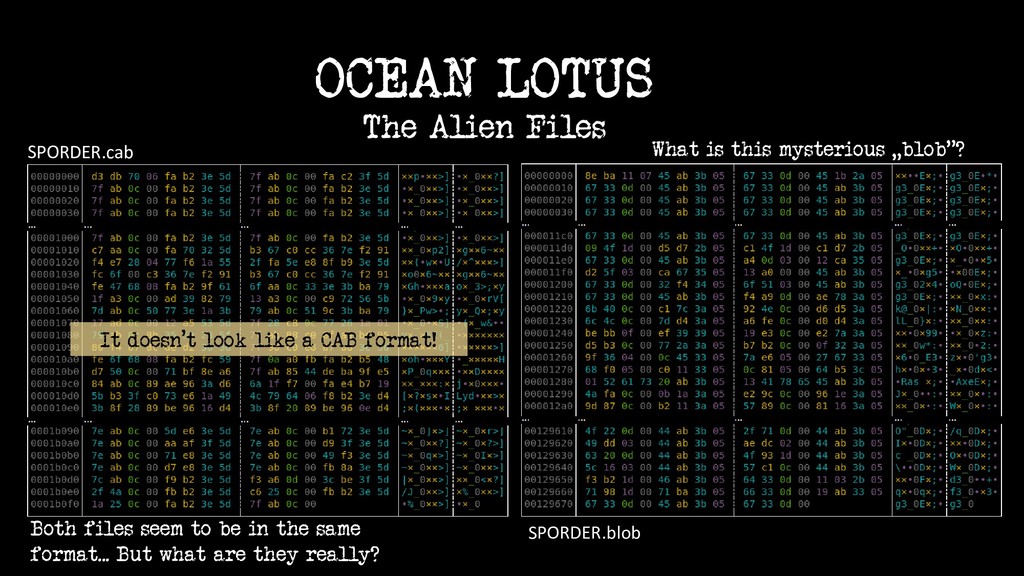
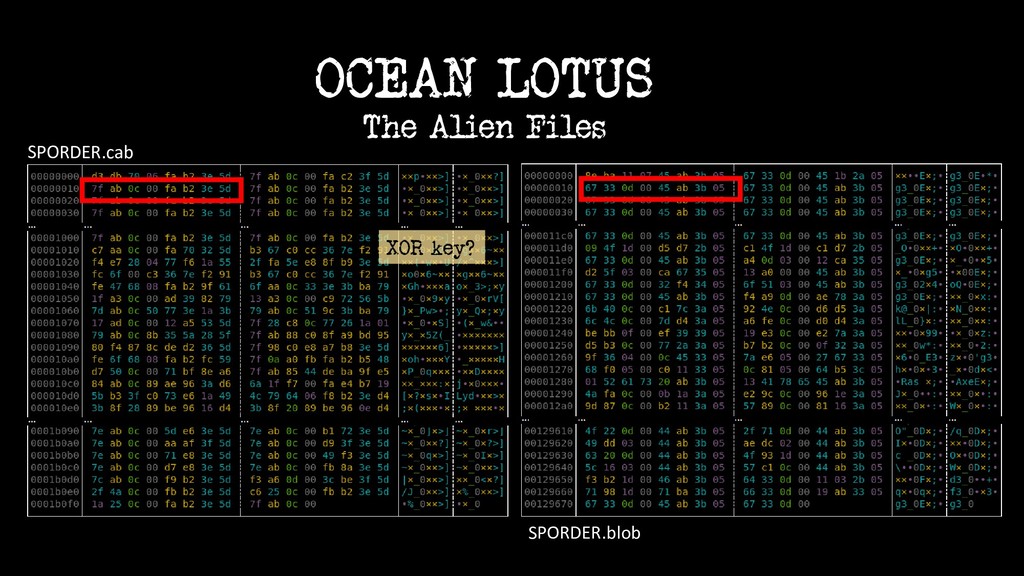
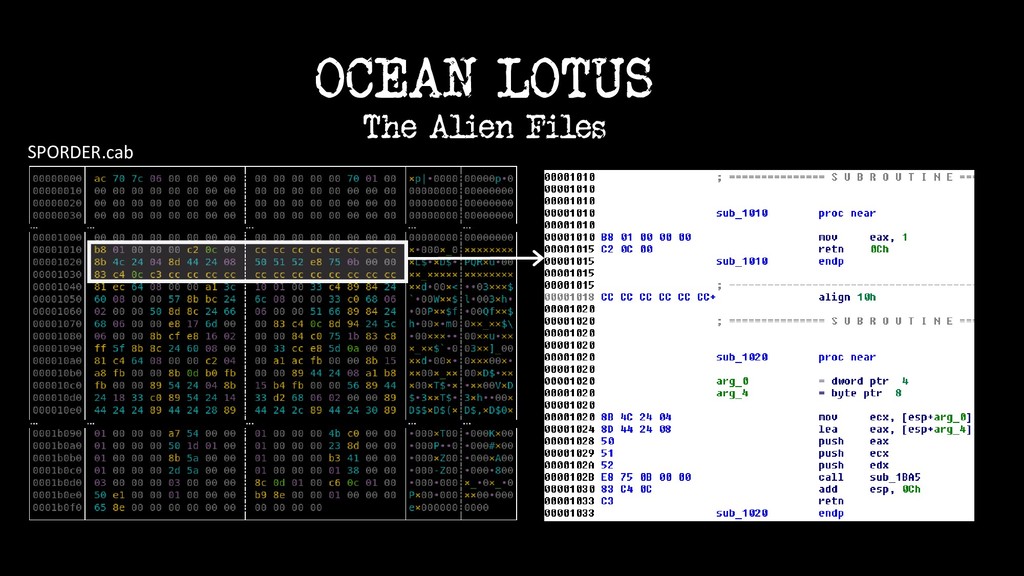
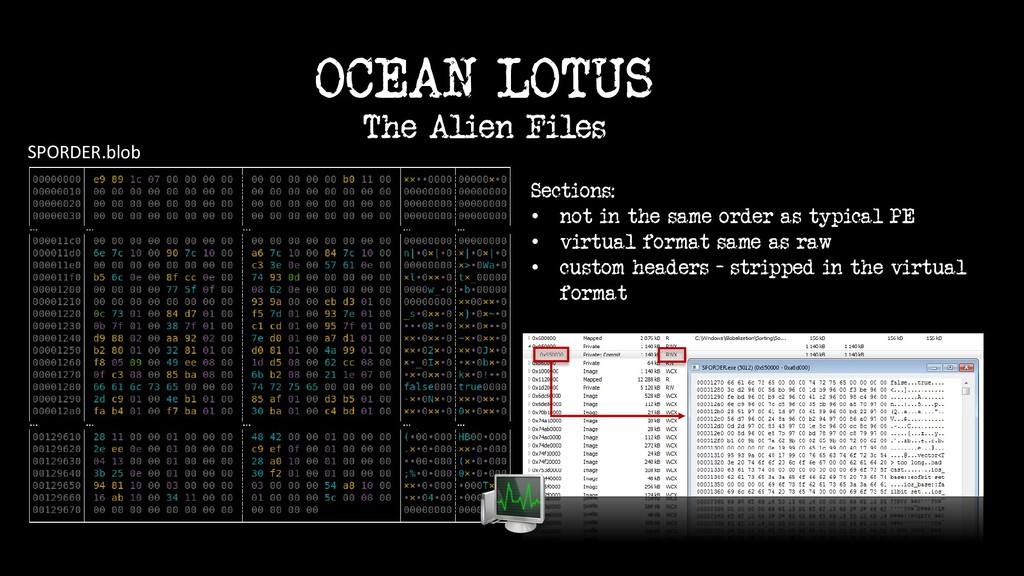
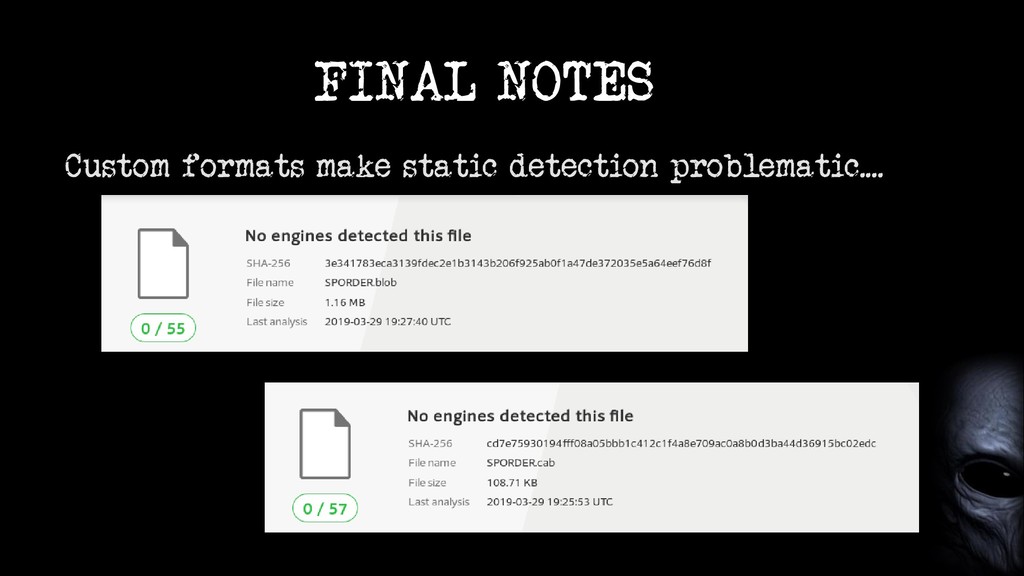
The Alien Files What is this mysterious „blob”? Both files
seem to be in the same format... But what are they really? SPORDER.cab It doesn’t look like a CAB format! SPORDER.blob OCEAN LOTUS -
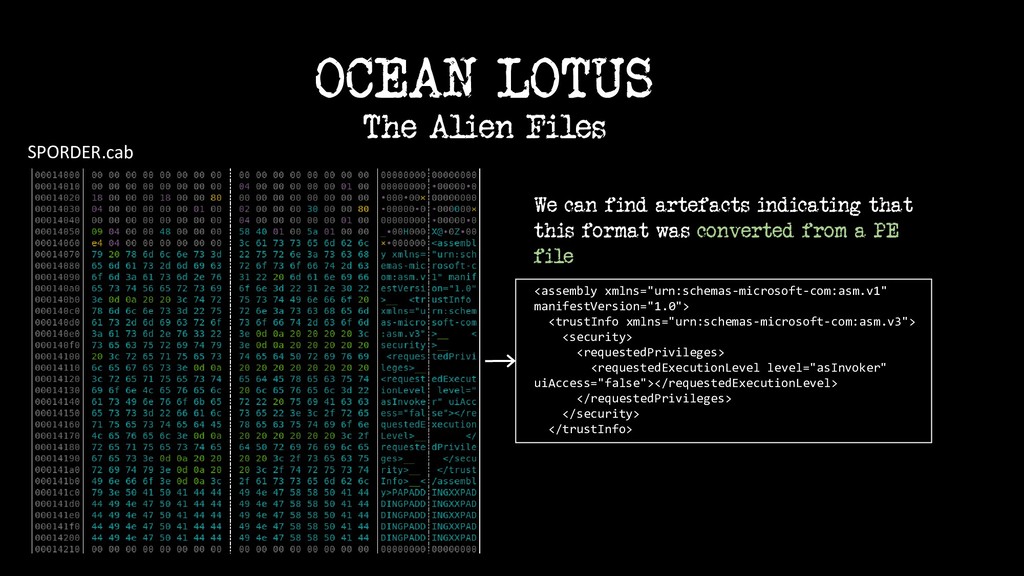
SPORDER.cab <assembly xmlns="urn:schemas-microsoft-com:asm.v1" manifestVersion="1.0"> <trustInfo xmlns="urn:schemas-microsoft-com:asm.v3"> <security> <requestedPrivileges> <requestedExecutionLevel level="asInvoker"
uiAccess="false"></requestedExecutionLevel> </requestedPrivileges> </security> </trustInfo> We can find artefacts indicating that this format was converted from a PE file OCEAN LOTUS The Alien Files -
SPORDER.blob Sections: • not in the same order as typical
PE • virtual format same as raw • custom headers - stripped in the virtual format OCEAN LOTUS The Alien Files -
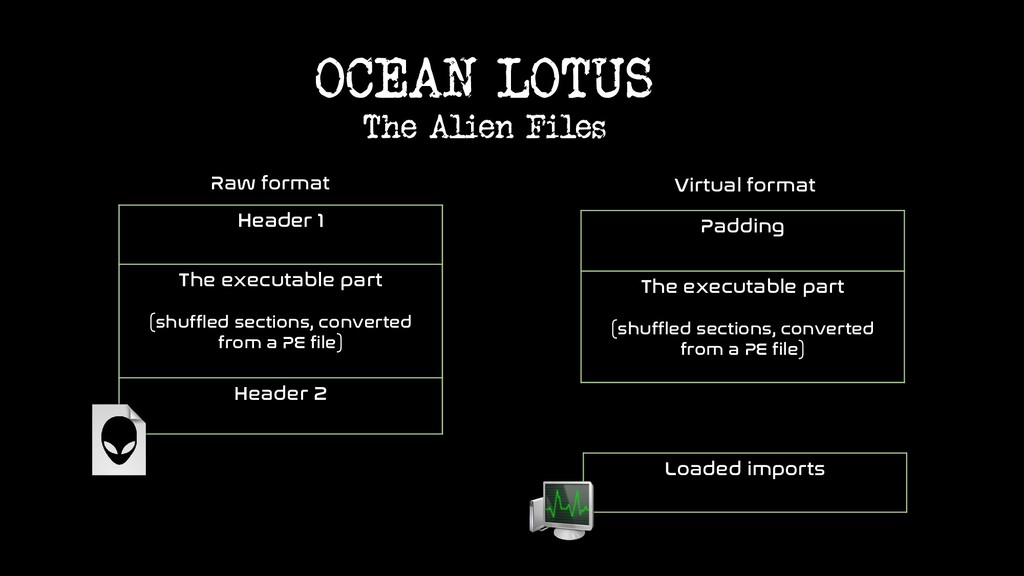
Raw format Header 1 The executable part (shuffled sections, converted
from a PE file) Header 2 Padding The executable part (shuffled sections, converted from a PE file) Loaded imports Virtual format OCEAN LOTUS The Alien Files -
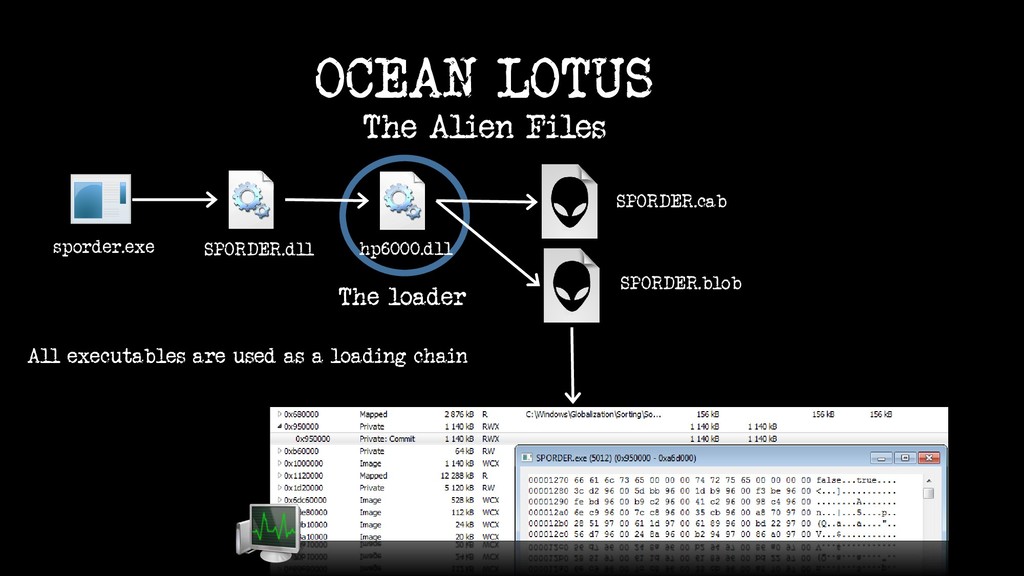
SPORDER.dll sporder.exe SPORDER.cab SPORDER.blob hp6000.dll OCEAN LOTUS The Alien Files
The loader All executables are used as a loading chain -
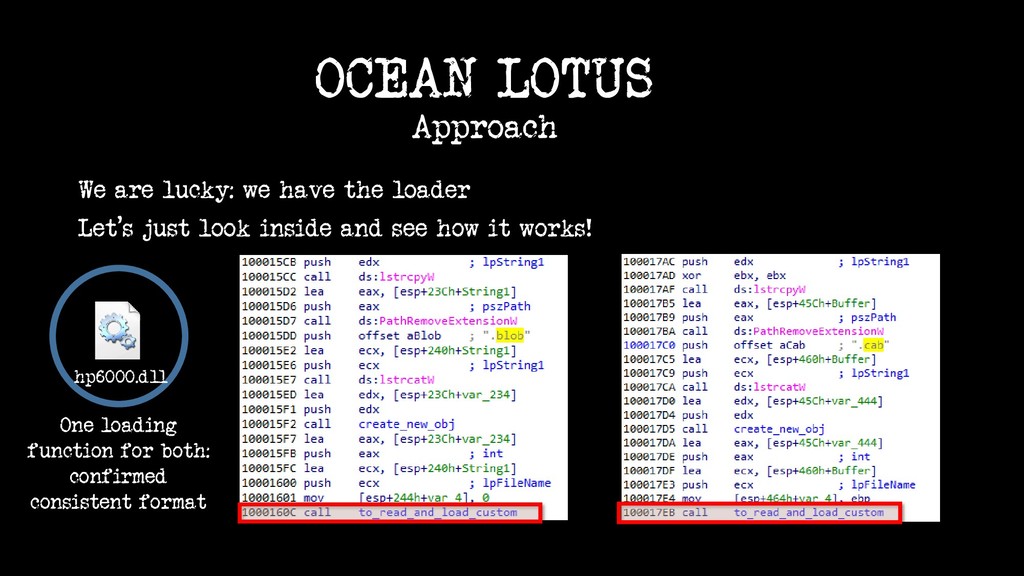
We are lucky: we have the loader Let’s just look
inside and see how it works! hp6000.dll One loading function for both: confirmed consistent format OCEAN LOTUS Approach -
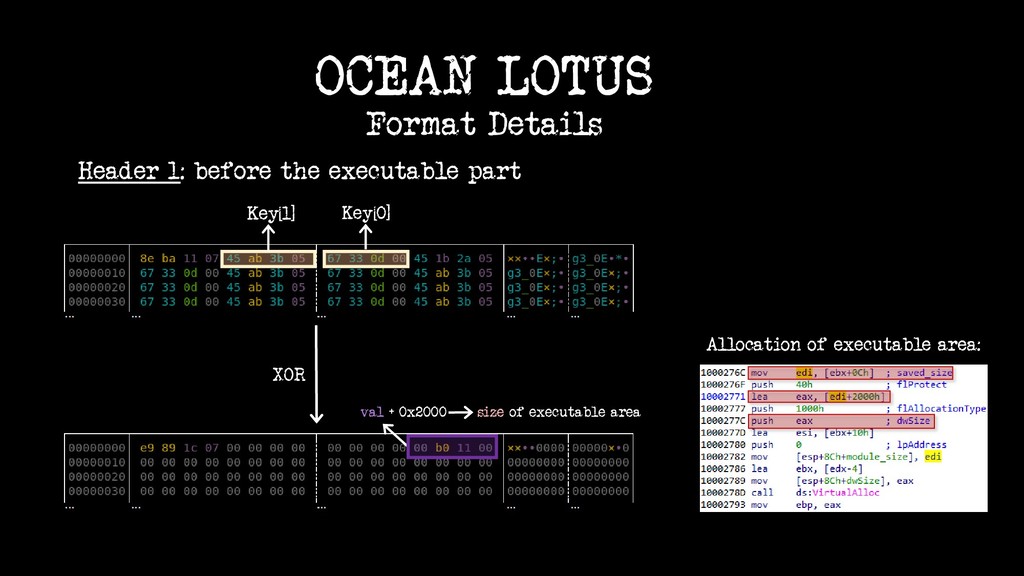
Header 1: before the executable part val + 0x2000 size
of executable area XOR OCEAN LOTUS Format Details Allocation of executable area: Key[1] Key[0] -
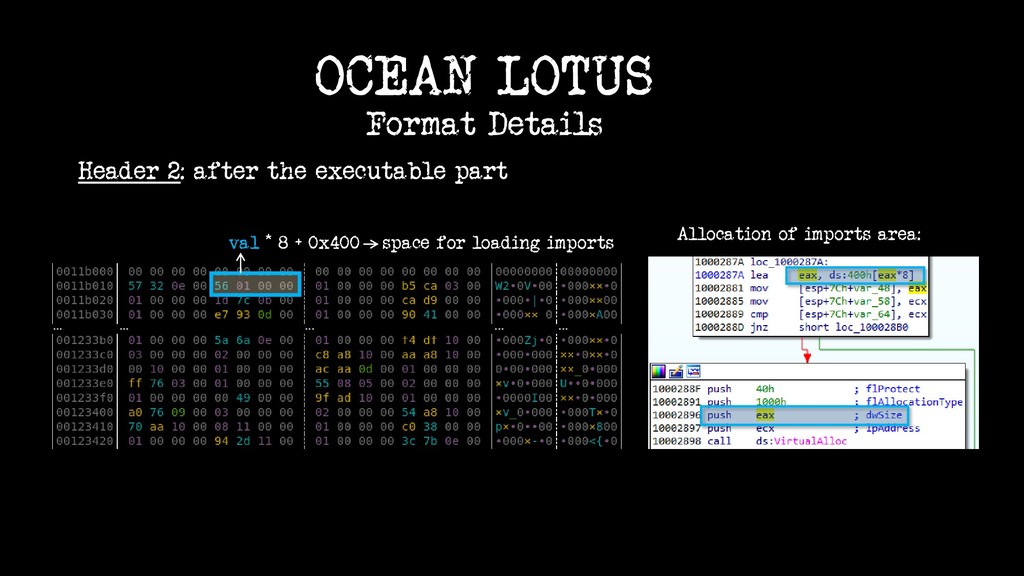
Header 2: after the executable part val * 8 +
0x400 space for loading imports OCEAN LOTUS Format Details Allocation of imports area: -
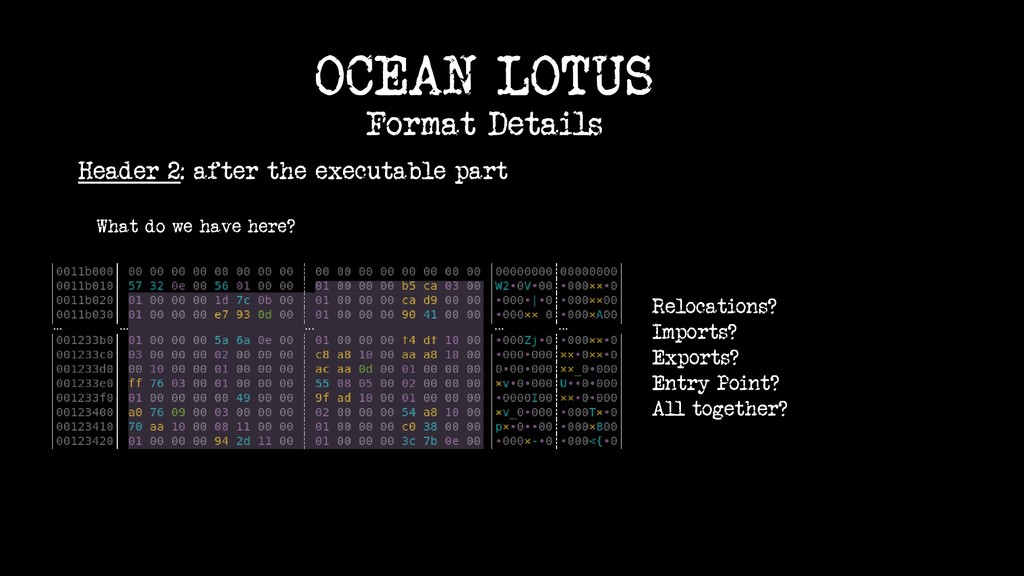
Relocations? Imports? Exports? Entry Point? All together? Header 2: after
the executable part OCEAN LOTUS Format Details What do we have here? -
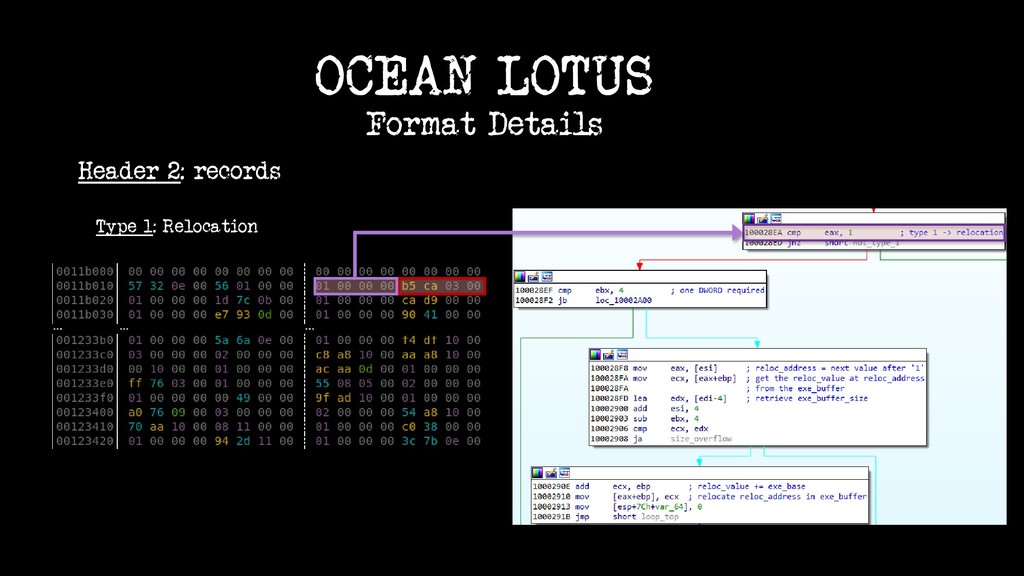
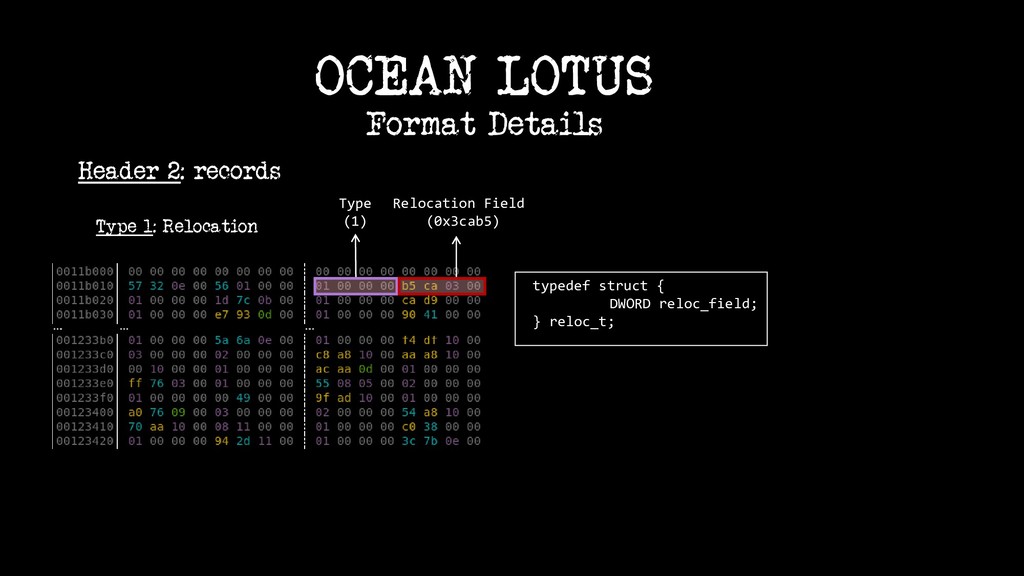
Relocation Field (0x3cab5) Header 2: records typedef struct { DWORD
reloc_field; } reloc_t; Type (1) OCEAN LOTUS Format Details Type 1: Relocation -
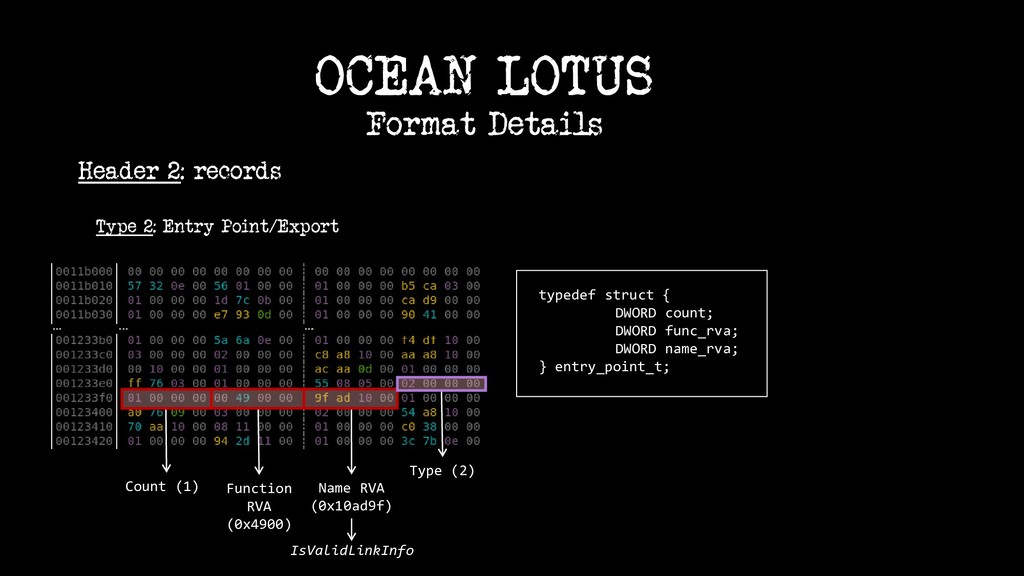
Header 2: records typedef struct { DWORD count; DWORD func_rva;
DWORD name_rva; } entry_point_t; OCEAN LOTUS Format Details Type 2: Entry Point/Export Count (1) Function RVA (0x4900) Name RVA (0x10ad9f) IsValidLinkInfo Type (2) -
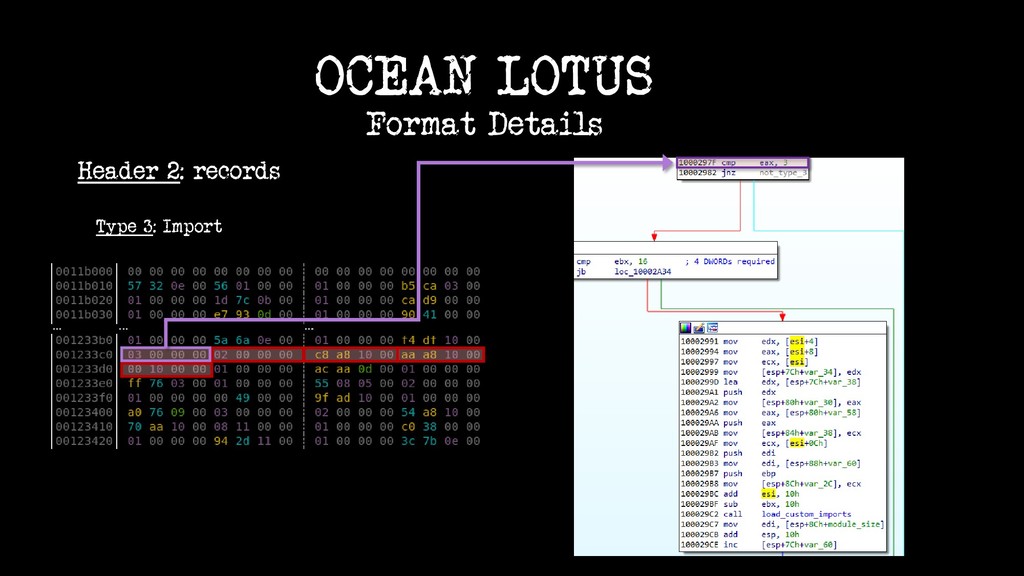
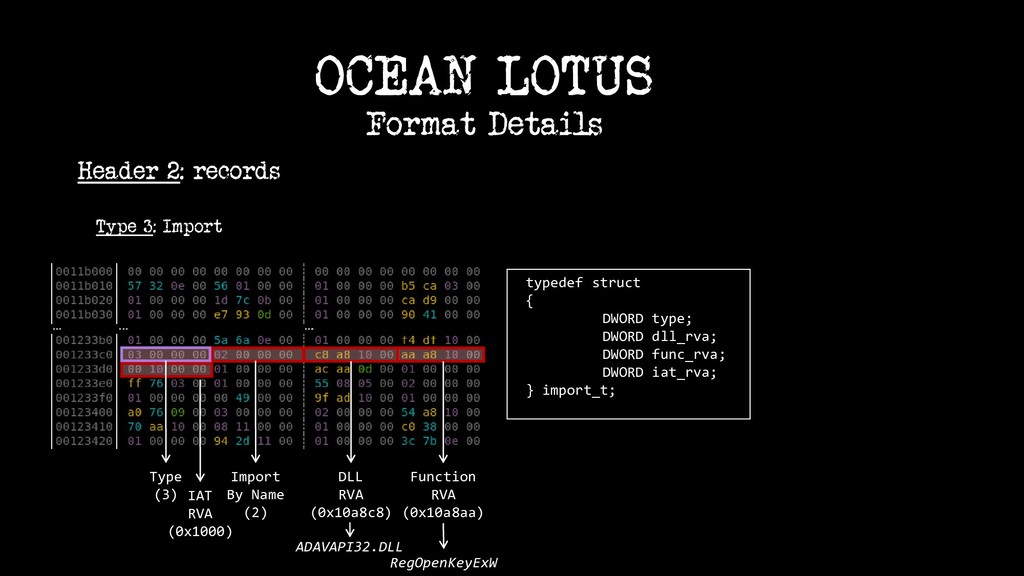
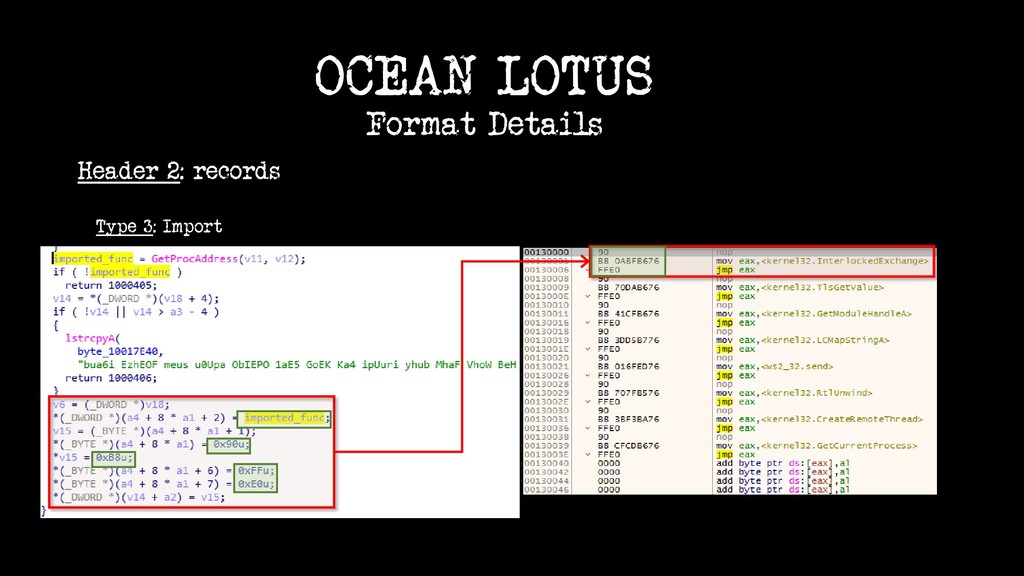
Header 2: records typedef struct { DWORD type; DWORD dll_rva;
DWORD func_rva; DWORD iat_rva; } import_t; OCEAN LOTUS Format Details Type 3: Import Type (3) IAT RVA (0x1000) Import By Name (2) DLL RVA (0x10a8c8) Function RVA (0x10a8aa) RegOpenKeyExW ADAVAPI32.DLL -
GOZI PE Like never seen before Overview • A popular
banking Trojan • Also known as: ISFB, Ursnif • Source code has been leaked and reused across multiple variants • We are going to discuss Gozi version 3 • Paper by Maciek Kotowicz’s (@maciekkotowicz): https://lokalhost.pl/txt/isfbv3.pdf -
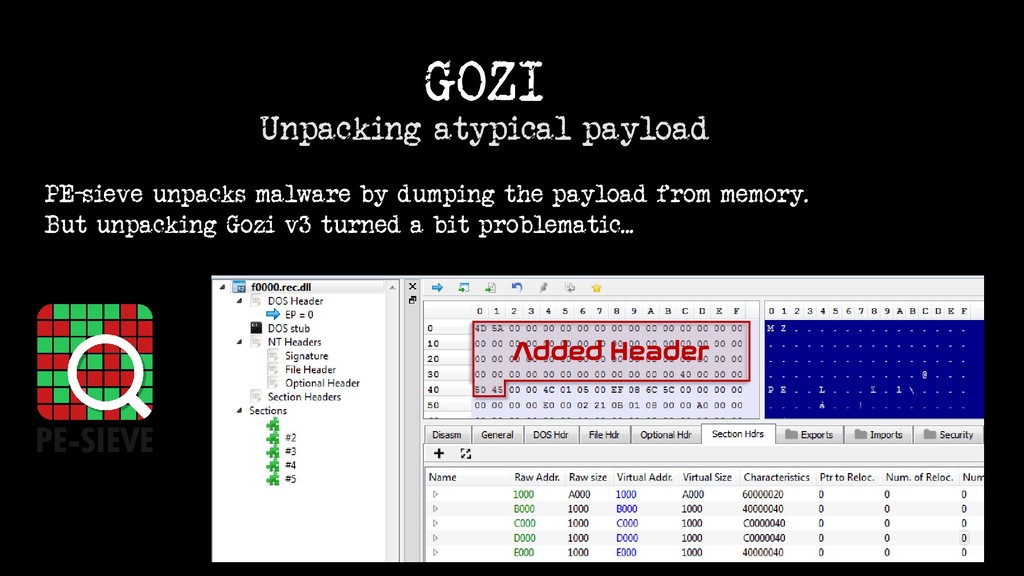
GOZI Unpacking atypical payload Added Header PE-sieve unpacks malware by
dumping the payload from memory. But unpacking Gozi v3 turned a bit problematic... -
• In the dumped PE, we are still missing: •
The Entry Point • Imports • Exports • Relocations • Let’s see how this PE looks in the memory, before it is mapped to the virtual format... GOZI -
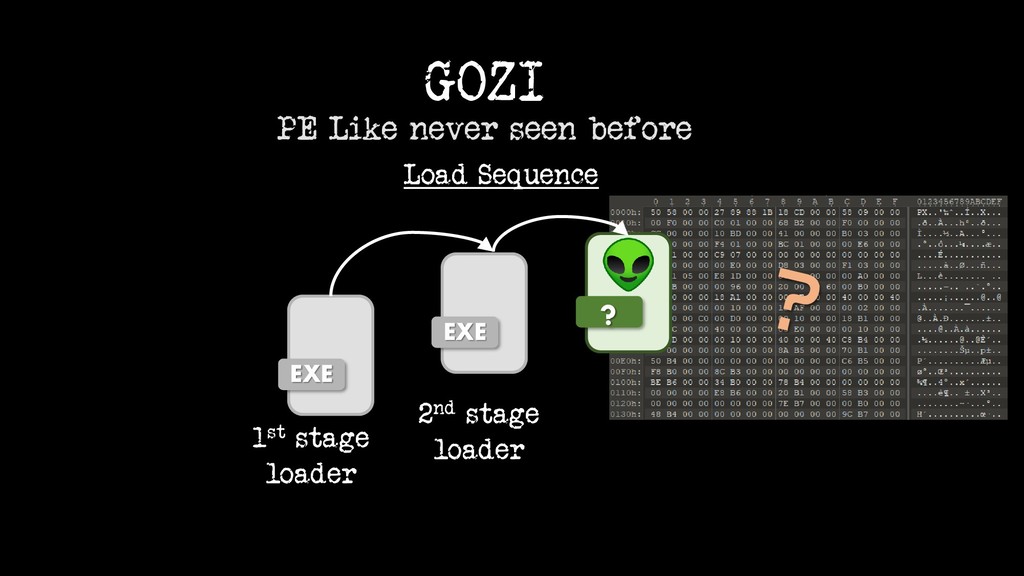
GOZI PE Like never seen before Load Sequence EXE EXE
1st stage loader 2nd stage loader ? -
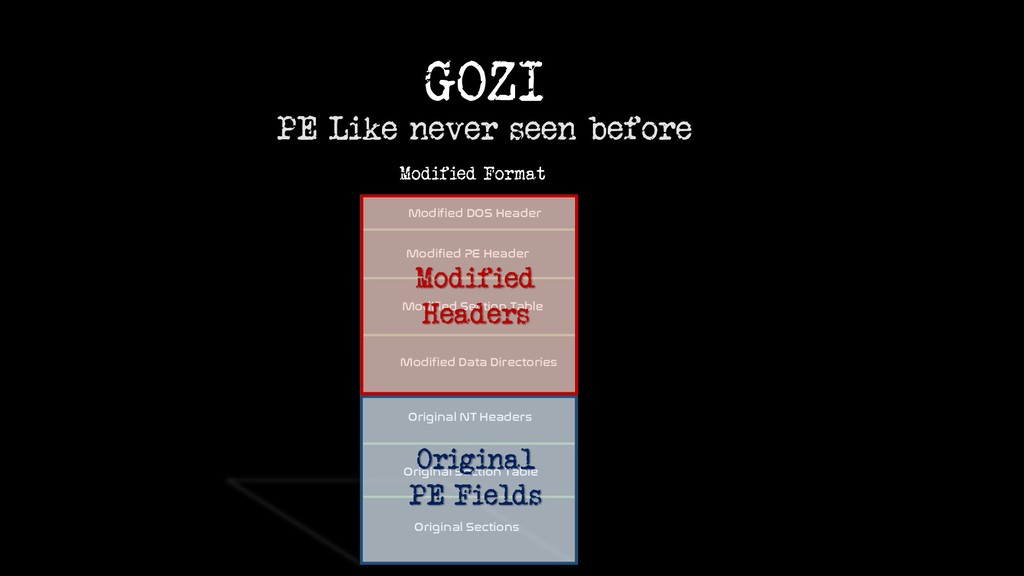
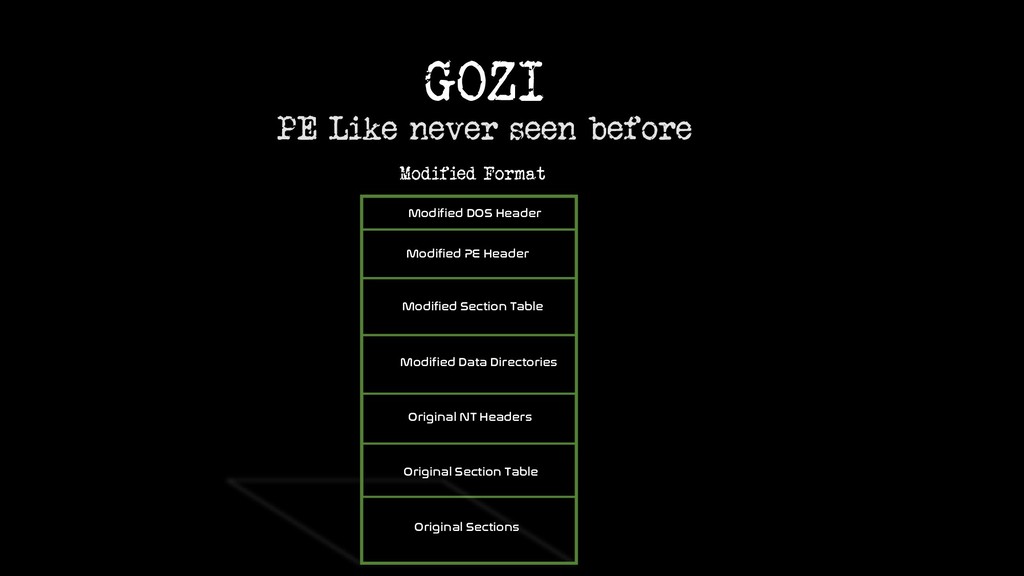
GOZI PE Like never seen before Modified Format Modified DOS
Header Modified Section Table Original Sections Original NT Headers Original Section Table Modified Data Directories Modified PE Header Modified Headers Original PE Fields -
GOZI PE Like never seen before Modified Format Modified DOS
Header Modified Section Table Original Sections Original NT Headers Original Section Table Modified Data Directories Modified PE Header -
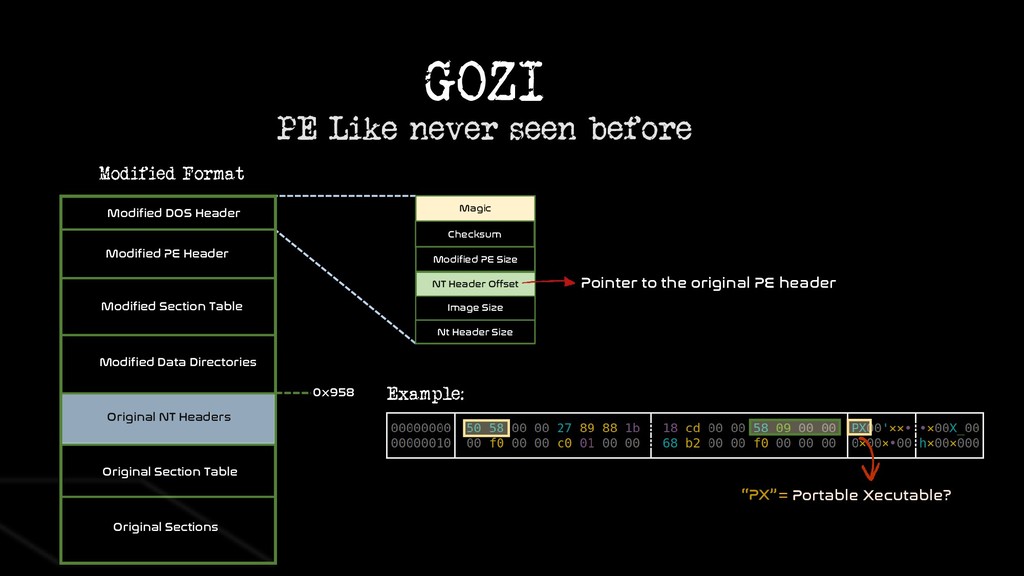
GOZI PE Like never seen before Magic Checksum NT Header
Offset Image Size Modified Format Magic NT Header Offset “PX” = Portable Xecutable? Modified PE Size Modified DOS Header Modified Section Table Original Sections Original NT Headers Original Section Table Modified Data Directories Modified PE Header Nt Header Size Example: Pointer to the original PE header Original NT Headers 0x958 -
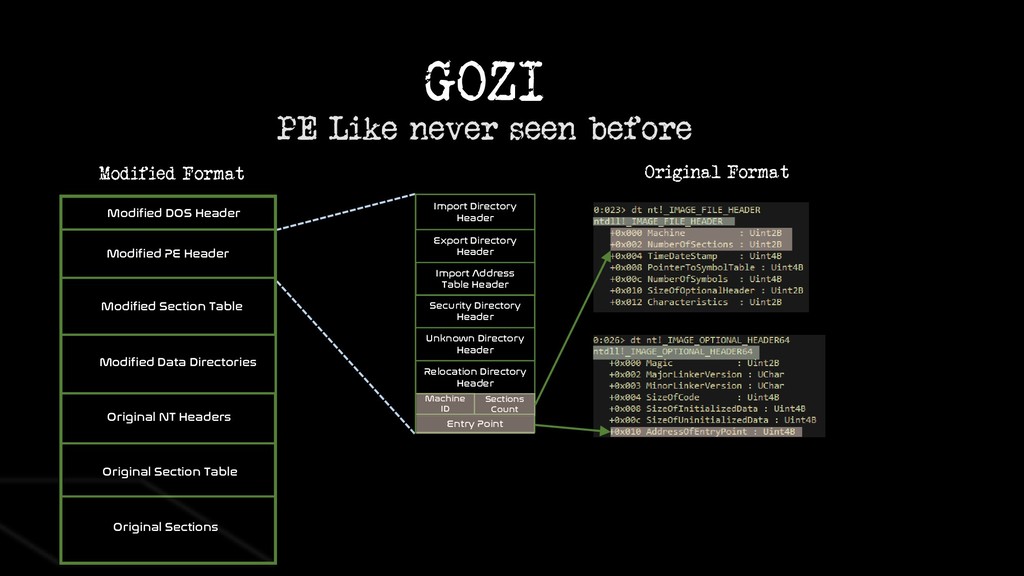
GOZI PE Like never seen before Modified DOS Header Modified
Format Modified Section Table Original Sections Original NT Headers Original Section Table Import Directory Header Export Directory Header Import Address Table Header Security Directory Header Unknown Directory Header Modified Data Directories Relocation Directory Header Modified PE Header Entry Point Machine ID Sections Count Original Format -
GOZI PE Like never seen before Modified DOS Header Modified
Format Modified Section Table Original Sections Original NT Headers Original Section Table Import Directory Header Export Directory Header Import Address Table Header Security Directory Header Unknown Directory Header Modified Data Directories Relocation Directory Header Modified PE Header Entry Point Machine ID Sections Count Original Format Modified Directory Headers • PX format contains only subset of the PE format directory headers • Order of appearance of directory headers is different -
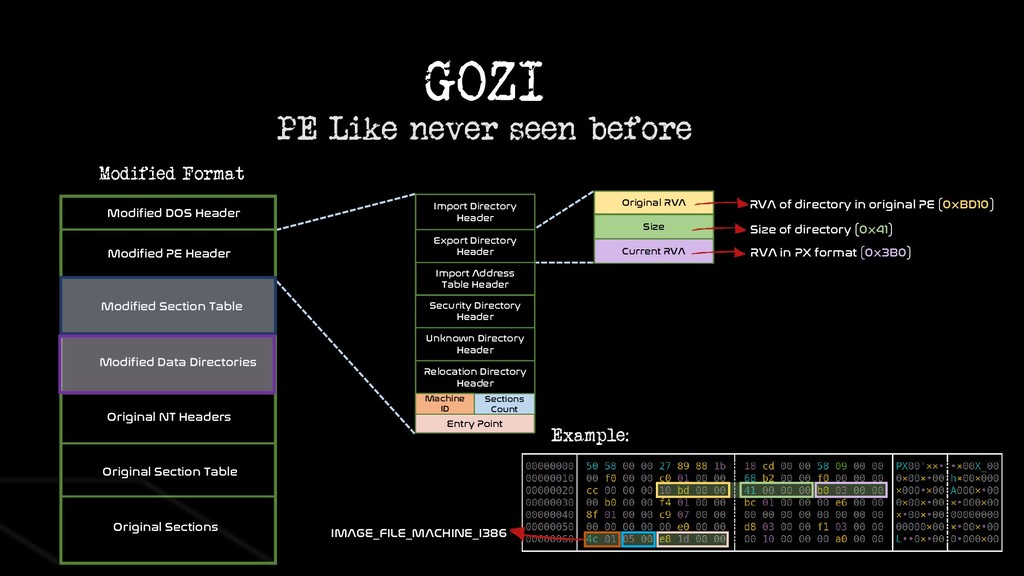
GOZI PE Like never seen before Original RVA Current RVA
Modified DOS Header Modified Format Modified Section Table Original Sections Original NT Headers Original Section Table Size Import Directory Header Export Directory Header Import Address Table Header Security Directory Header Unknown Directory Header Modified Data Directories Relocation Directory Header Modified PE Header Original RVA Size Current RVA Entry Point Machine ID Sections Count Entry Point Machine ID Sections Count Example: RVA of directory in original PE (0xBD10) Size of directory (0x41) RVA in PX format (0x3B0) IMAGE_FILE_MACHINE_I386 -
GOZI PE Like never seen before • Attempt to revive
the PE format with a new “flavor” • To recover the original PE, we need to dump the PX format, and use the converter https://github.com/hasherezade/funky_malware_parsers/ tree/master/isfb_parser EXE PX -
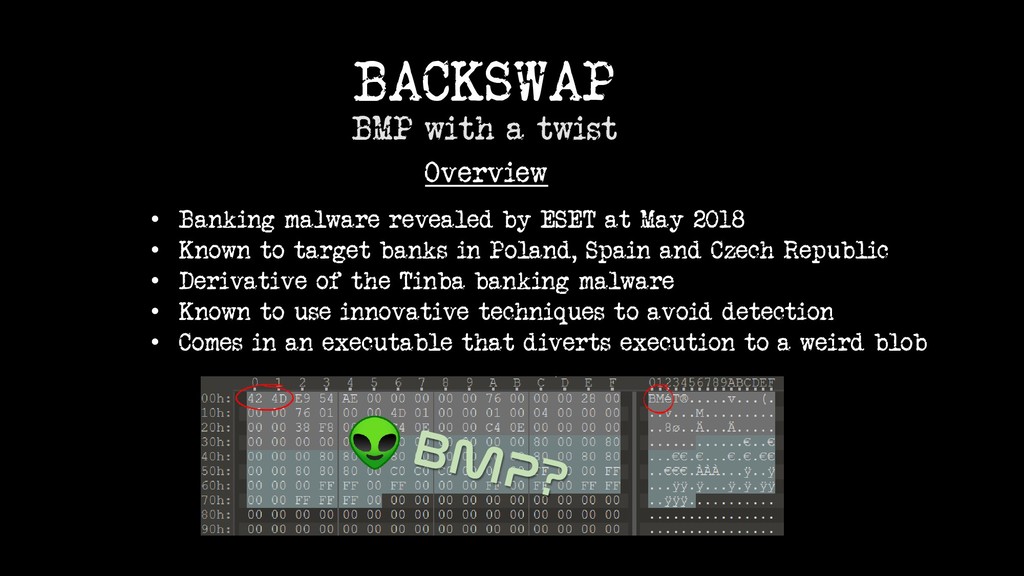
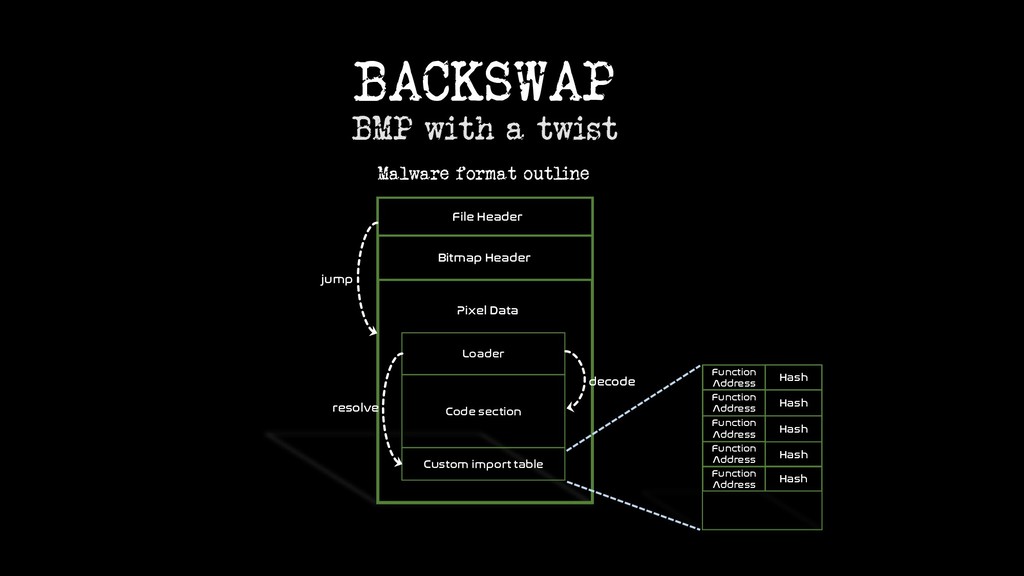
BACKSWAP BMP with a twist Overview • Banking malware revealed
by ESET at May 2018 • Known to target banks in Poland, Spain and Czech Republic • Derivative of the Tinba banking malware • Known to use innovative techniques to avoid detection • Comes in an executable that diverts execution to a weird blob -
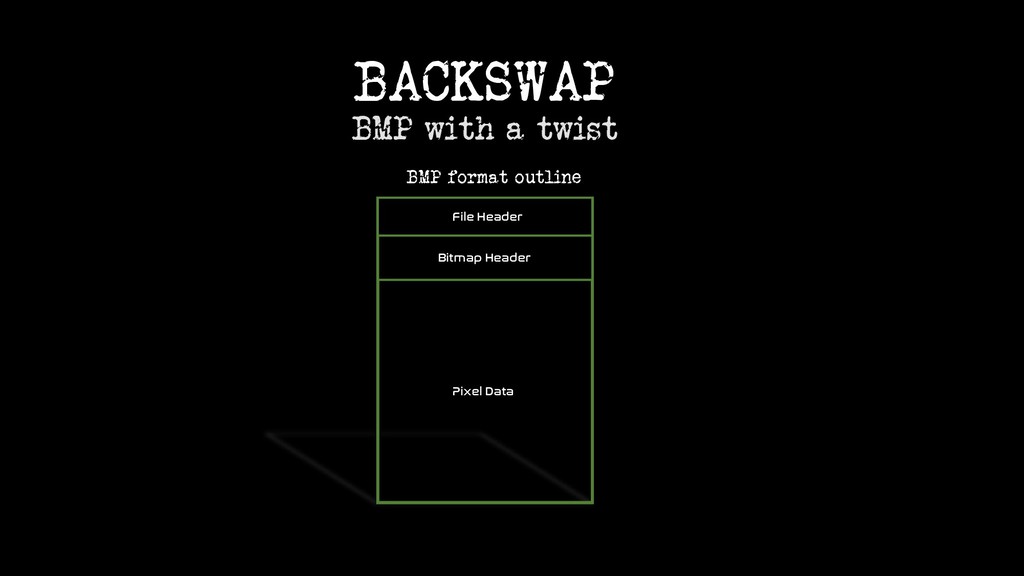
BACKSWAP BMP with a twist Bitmap Header Pixel Data File
Header BMP format outline -
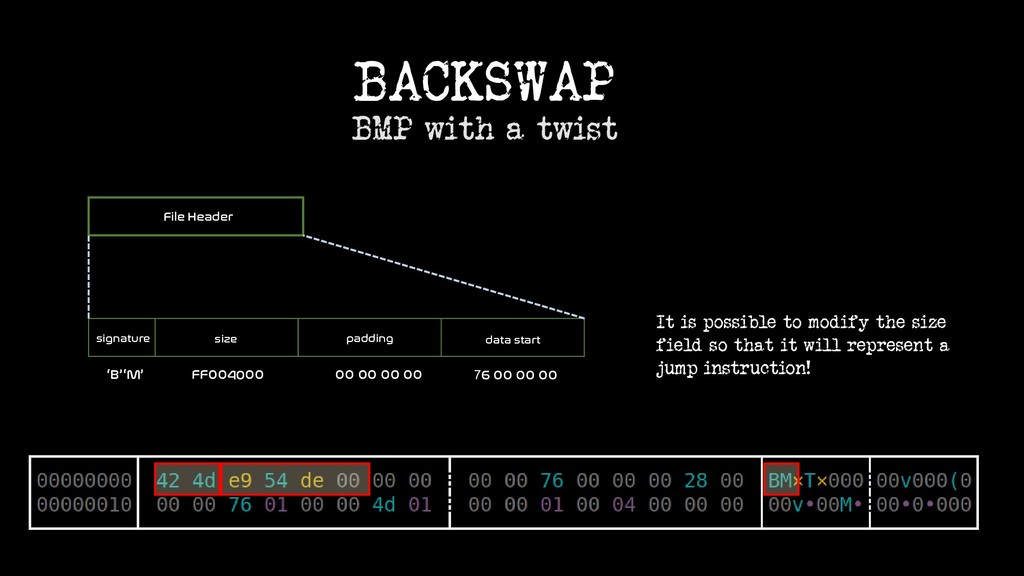
BACKSWAP BMP with a twist File Header signature size padding
data start ‘B’‘M’ 00 00 00 00 76 00 00 00 FF004000 -
BACKSWAP BMP with a twist File Header signature size padding
data start ‘B’ 00 00 00 00 76 00 00 00 FF004000 ‘M’ It is possible to modify the size field so that it will represent a jump instruction! -
DE 54 E9 42 4D BACKSWAP BMP with a twist
File Header signature size padding data start INC EDX DEC EBP 00 00 00 00 76 00 00 00 00 00 JMP offset It is possible to modify the size field so that it will represent a jump instruction! -
BACKSWAP BMP with a twist Loader Code section Custom import
table resolve decode Function Address Hash Function Address Hash Function Address Hash Function Address Hash Function Address Hash Bitmap Header Pixel Data File Header jump Malware format outline -
BACKSWAP BMP with a twist Loader Code section Custom import
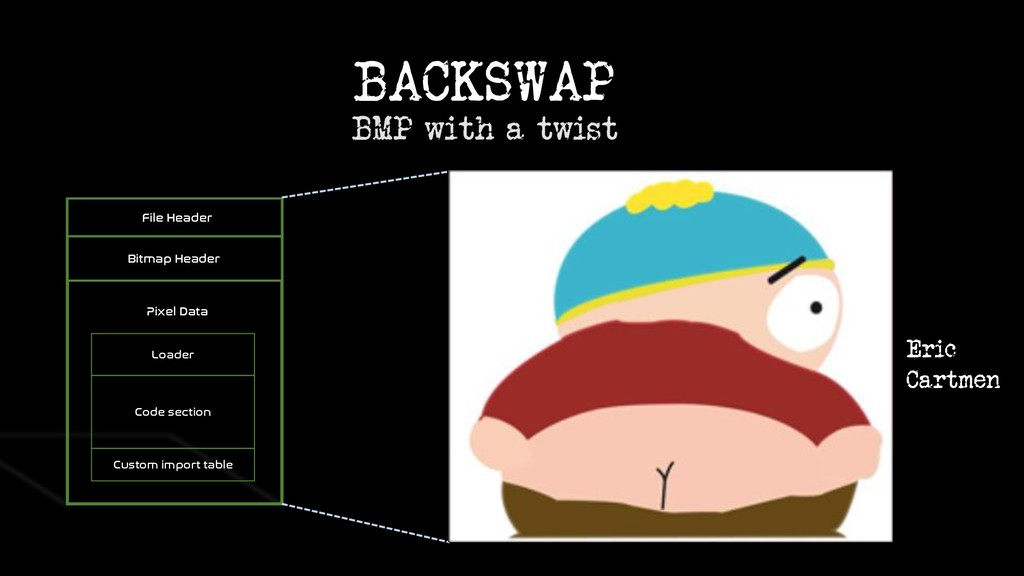
table Bitmap Header Pixel Data File Header When we try to visualize the BMP, we realize it’s a polyglot polyglot binary represented by several formats, depending on how you look at it @angealbertini -
BACKSWAP BMP with a twist Loader Code section Custom import
table Bitmap Header Pixel Data File Header Malware Payload -
BACKSWAP BMP with a twist Loader Code section Custom import
table Bitmap Header Pixel Data File Header Malware Payload Eric Cartmen -
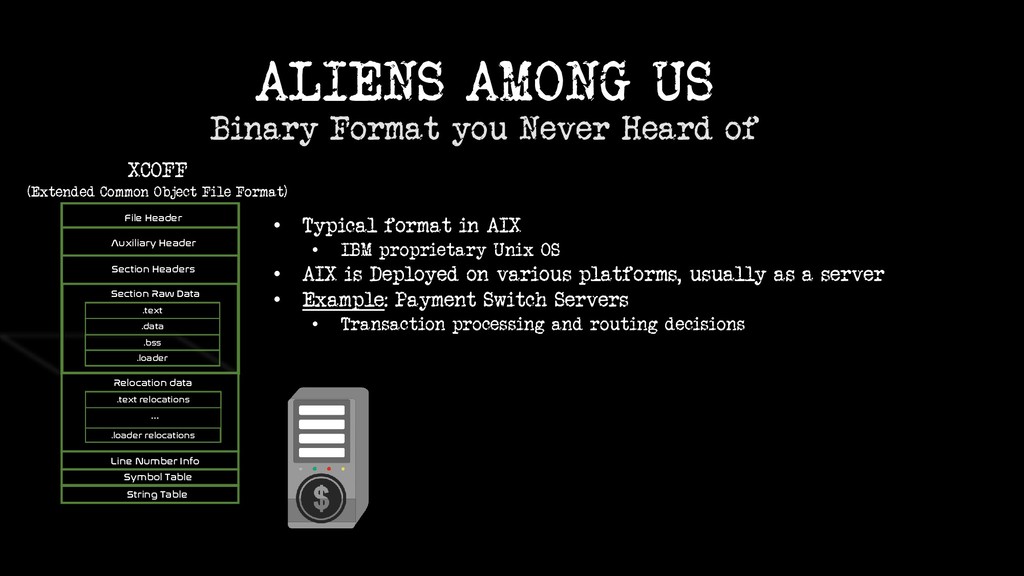
ALIENS AMONG US Binary Format you Never Heard of •
Typical format in AIX • IBM proprietary Unix OS • AIX is Deployed on various platforms, usually as a server • Example: Payment Switch Servers • Transaction processing and routing decisions Auxiliary Header File Header .text .bss Section Raw Data Section Headers .text relocations .loader relocations Relocation data … XCOFF (Extended Common Object File Format) .data .loader Line Number Info Symbol Table String Table -
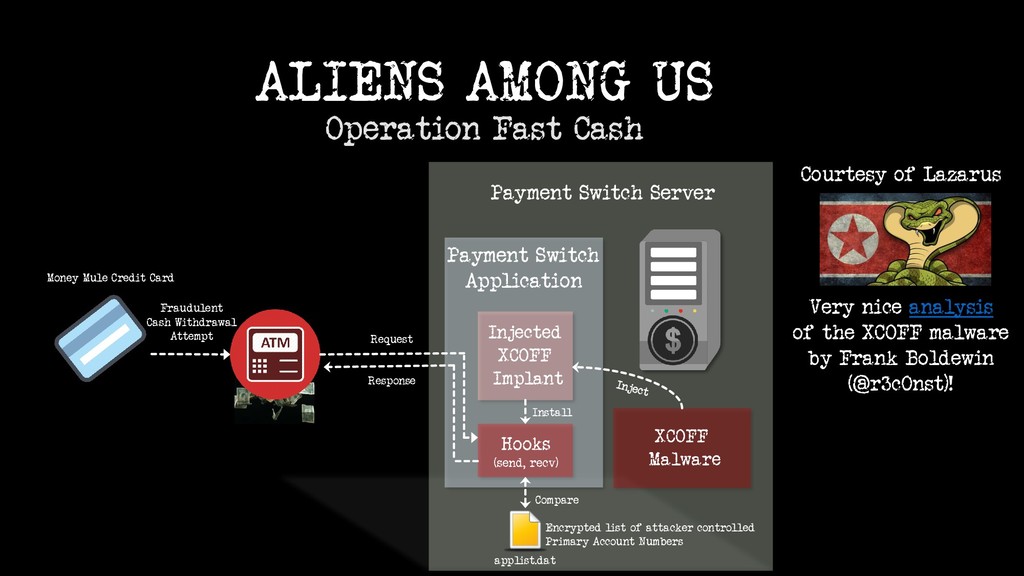
ALIENS AMONG US Operation Fast Cash Payment Switch Server Payment
Switch Application Injected XCOFF Implant XCOFF Malware Hooks (send, recv) Install Compare Request Response applist.dat Encrypted list of attacker controlled Primary Account Numbers Fraudulent Cash Withdrawal Attempt Courtesy of Lazarus Money Mule Credit Card Very nice analysis of the XCOFF malware by Frank Boldewin (@r3c0nst)! -
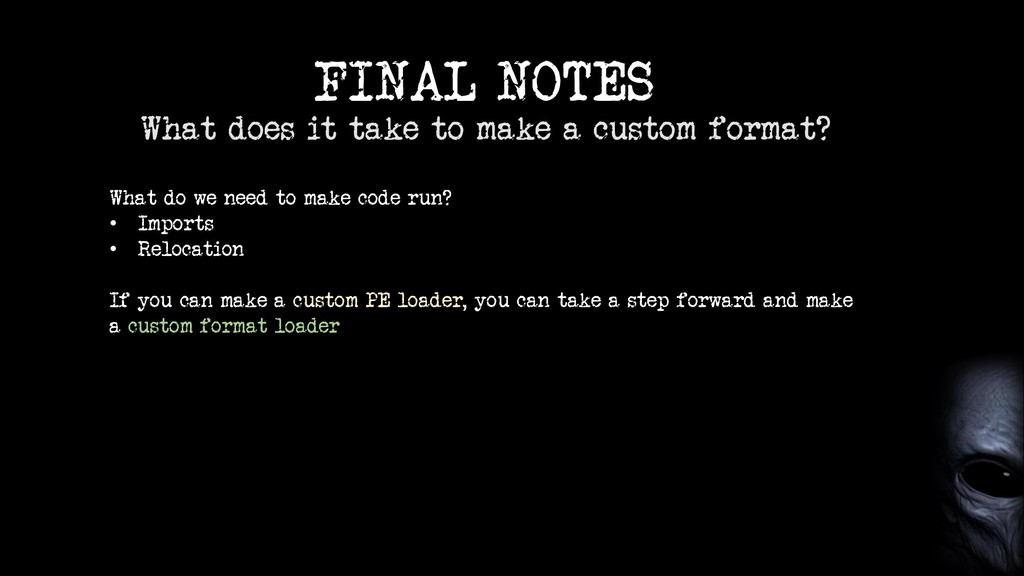
FINAL NOTES What does it take to make a custom
format? What do we need to make code run? • Imports • Relocation If you can make a custom PE loader, you can take a step forward and make a custom format loader -
APPENDIX • Malware analysis of Hidden Bee’s custom format, by
Aleksandra (@hasherezade): • https://blog.malwarebytes.com/threat-analysis/2018/08/reversing-malware-in-a- custom-format-hidden-bee-elements/ • Paper by Maciek Kotowicz’s (@maciekkotowicz) on Gozi custom format: https://lokalhost.pl/txt/isfbv3.pdf • Backswap publication by Itay Cohen (@megabeets_): • https://research.checkpoint.com/the-evolution-of-backswap/ • Analysis of Lazarus XCOFF malware (Operation Fast Cash) by Frank Boldewin: • https://github.com/fboldewin/FastCashMalwareDissected/blob/master/Operation %20Fast%20Cash%20- %20Hidden%20Cobra%E2%80%98s%20AIX%20PowerPC%20malware%20dissected. pdf • Github repository with tools for analyzing the discussed formats: https://github.com/hasherezade/funky_malware_parsers