Share
Embed
Security Case Study 2016: Petya - taking ransomware to the low level
hasherezade
September 14, 2016
Transcript
37 slides
-
Agenda •Ransomware – introduction and overview •Petya – what is
different? •Brief analysis •Walk throught the evolution •Defeating the first version •Defeating the second version •Status for today -
Ransomware – introduction and overview General idea: Forcing a victim
to pay the ransom by blocking access to the files The most popular type of malware this year -
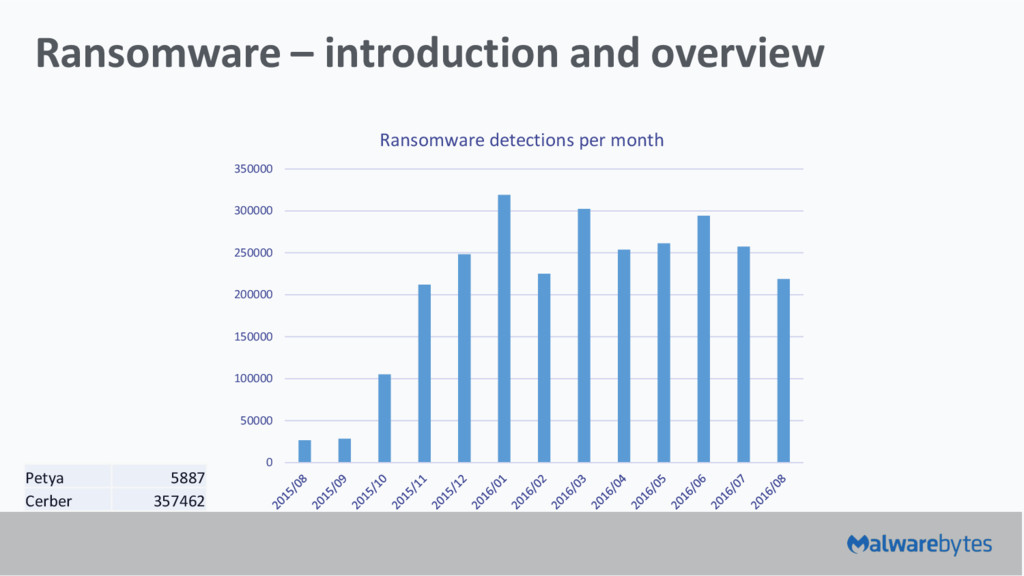
Ransomware – introduction and overview 0 50000 100000 150000 200000
250000 300000 350000 Ransomware detections per month Petya 5887 Cerber 357462 -
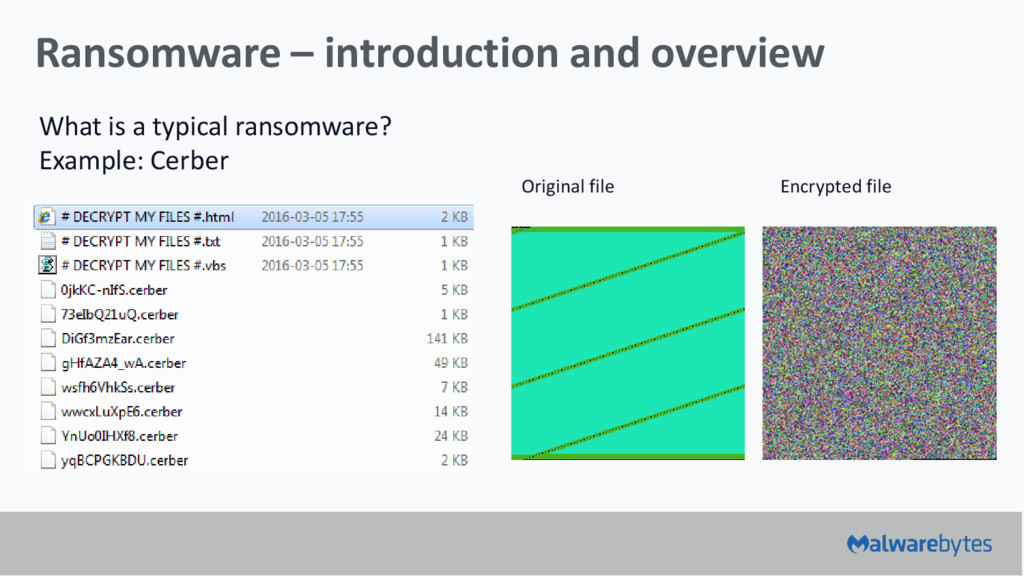
Ransomware – introduction and overview What is a typical ransomware?
Example: Cerber Original file Encrypted file -
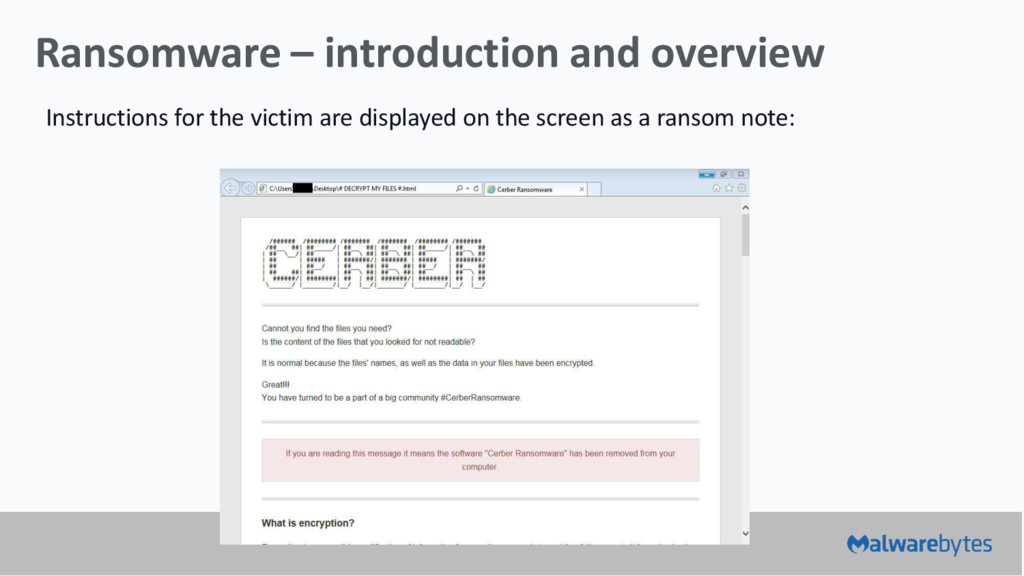
Ransomware – introduction and overview Instructions for the victim are
displayed on the screen as a ransom note: -
Ransomware – introduction and overview So many types! Easy to
get lost... https://id-ransomware.malwarehunterteam.com -
Almost all the ransomware encrypts files one by one Petya
attacks bootloader, and then encrypts low-level structures on the disk (Master File Table) – making files inaccessible Petya – how is it different? -
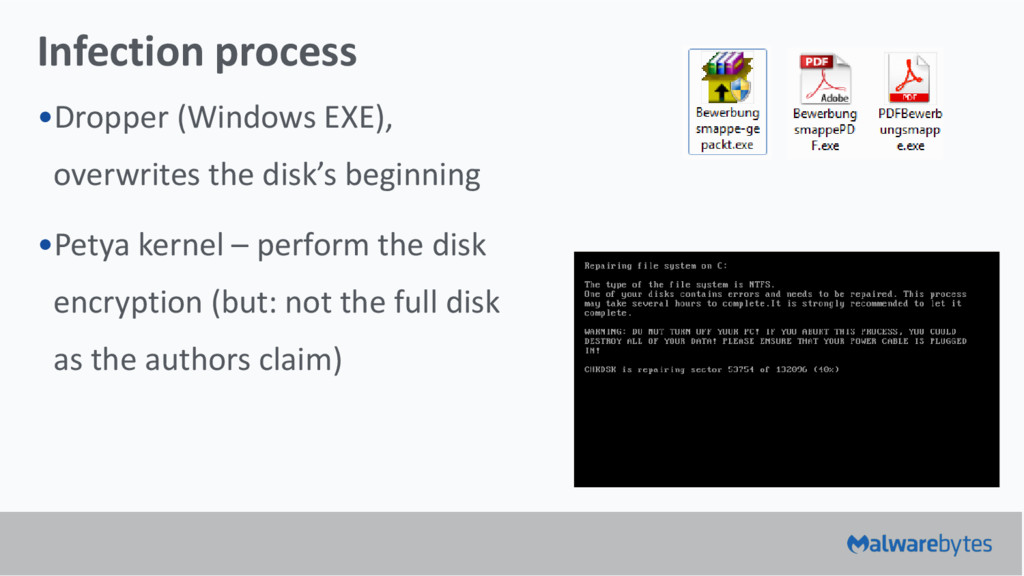
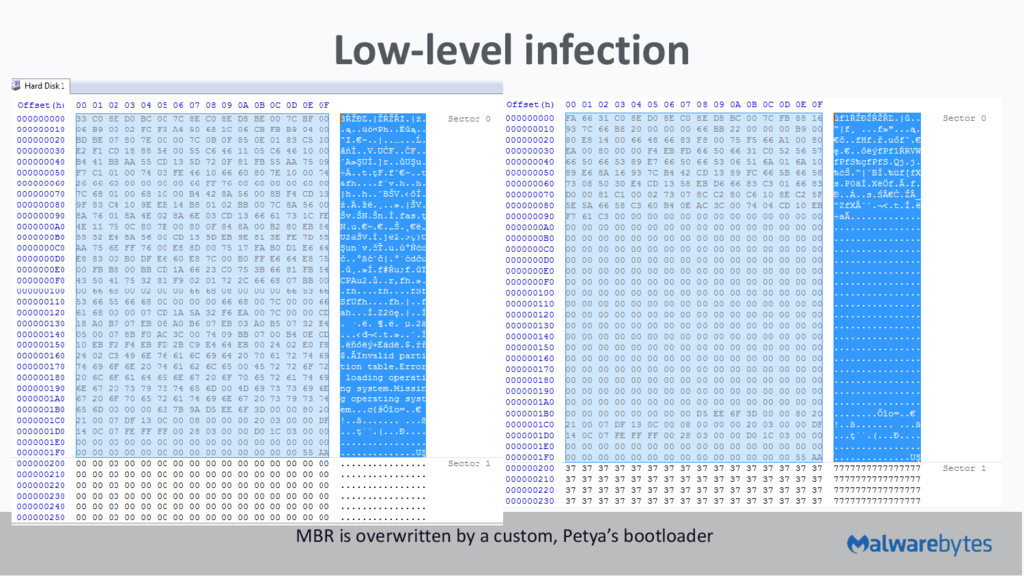
Infection process •Dropper (Windows EXE), overwrites the disk’s beginning •Petya
kernel – perform the disk encryption (but: not the full disk as the authors claim) -
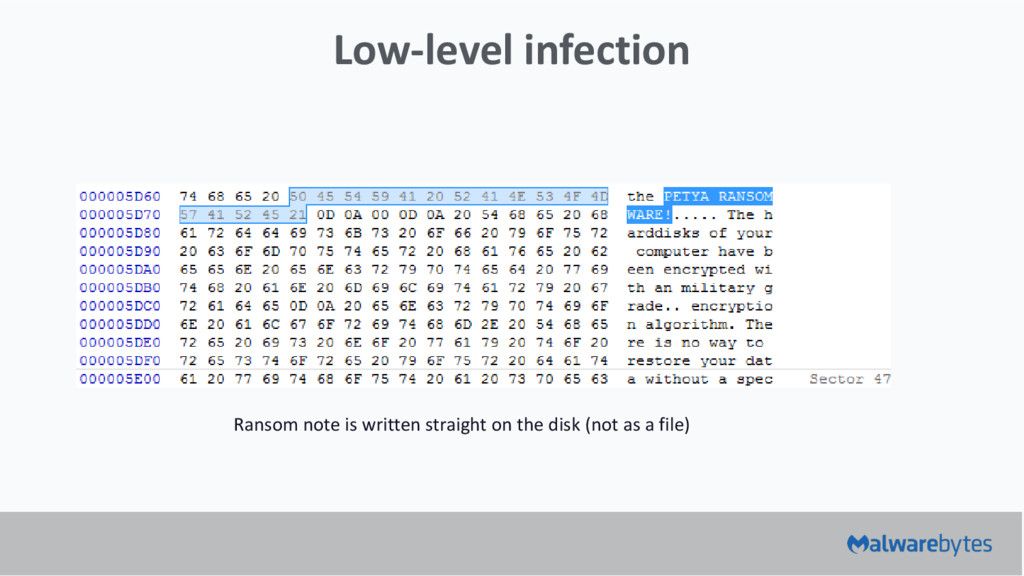
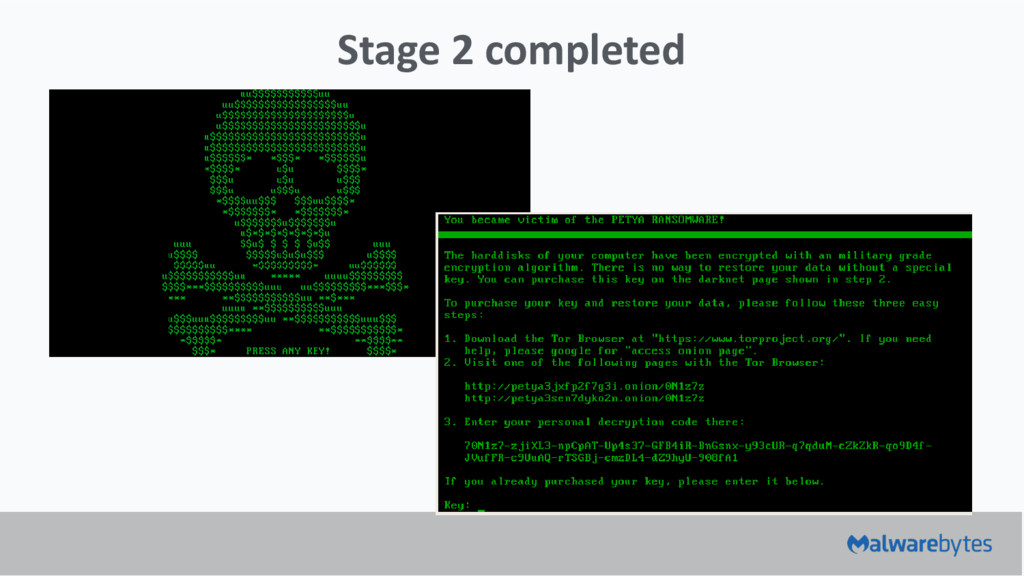
Low-level infection Ransom note is written straight on the disk
(not as a file) -
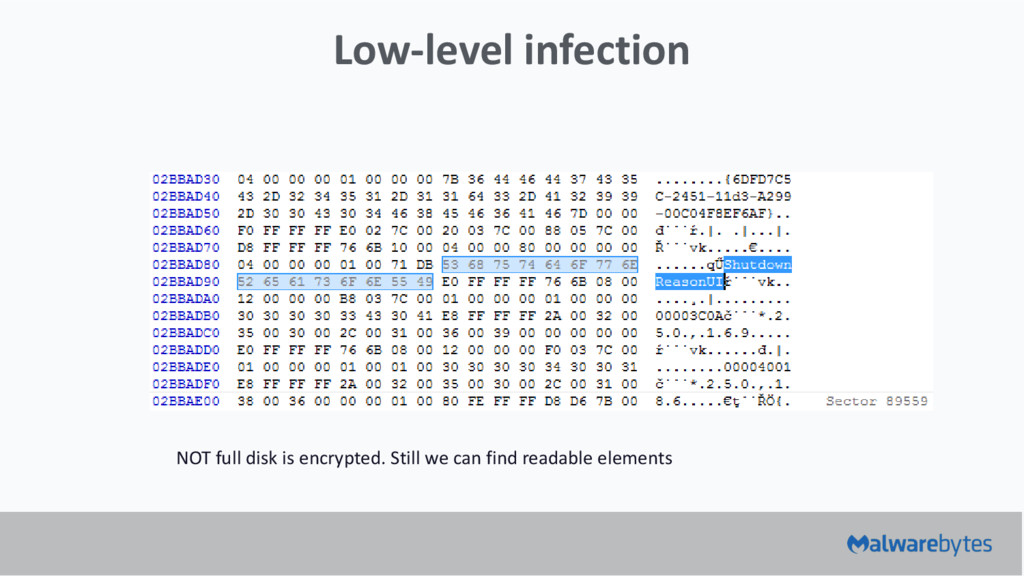
Low-level infection NOT full disk is encrypted. Still we can
find readable elements -
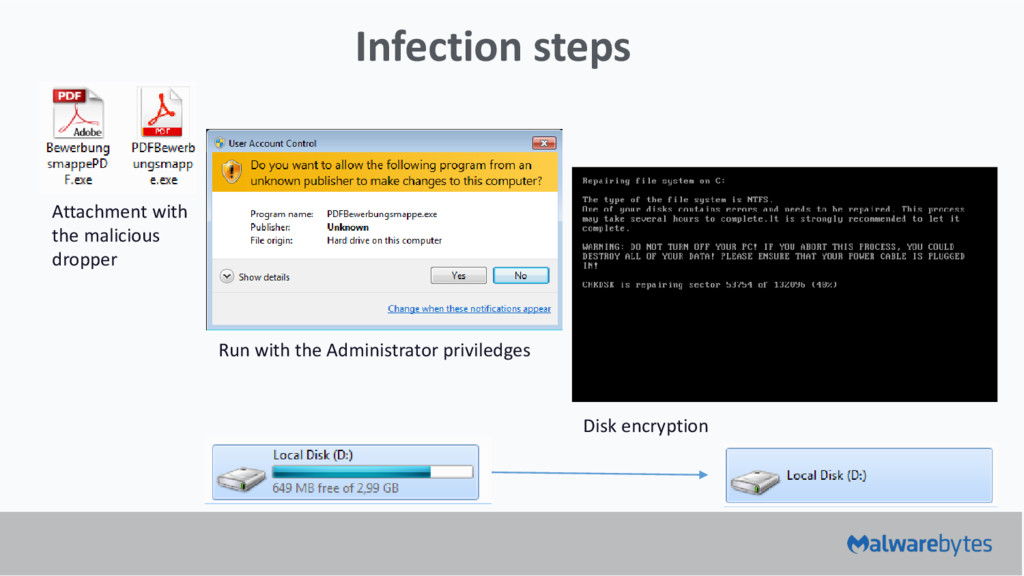
Infection steps Attachment with the malicious dropper Run with the
Administrator priviledges Disk encryption -
• Generates 16 byte long random key – it will
be used for disk encryption • Encrypts that random key by a hardcoded public key • Converts encrypted content into Base58 • Encrypts MBR by XOR z 0x7 (0x37 in version 1) and moves it into another sector • Overwrites disk’s beginning with Petya’s code • Overwrites MBR with custom bootloader • Prepares verification sector • Prepares data sector storing: generated random key and it’s encrypted form (will be displayed later as the user ID), etc Stage 1: dropper -
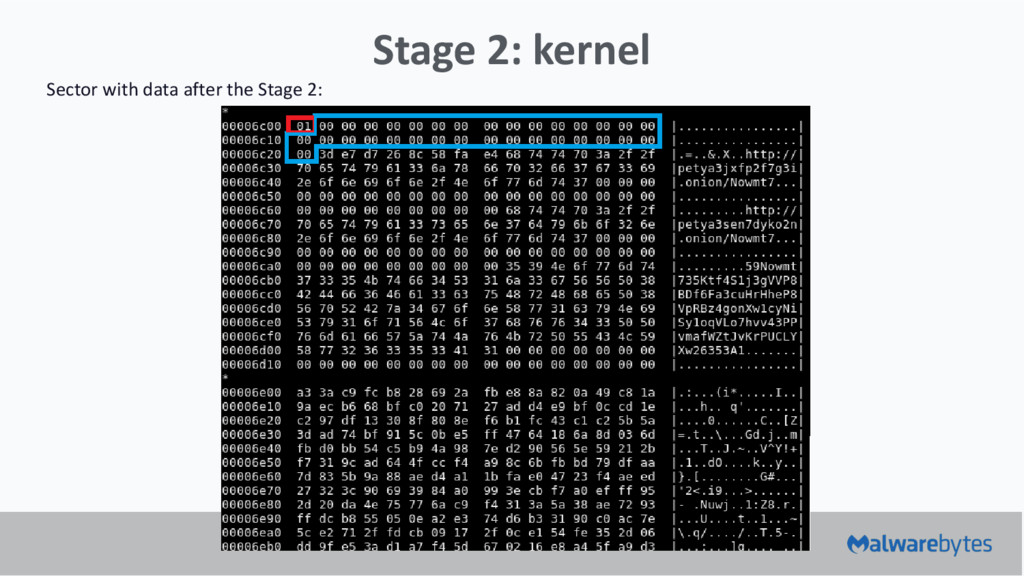
Stage 1: dropper Sector with data written to the disk
by the dropper (at Stage 1): -
Stage 2: kernel • Fetches to the memory the key
generated in the Stage 1 • Erase that key from the data sector • Encrypts verification sector and the next part of the disk (MFT) with the help of given key and the algorithm Salsa 20 -
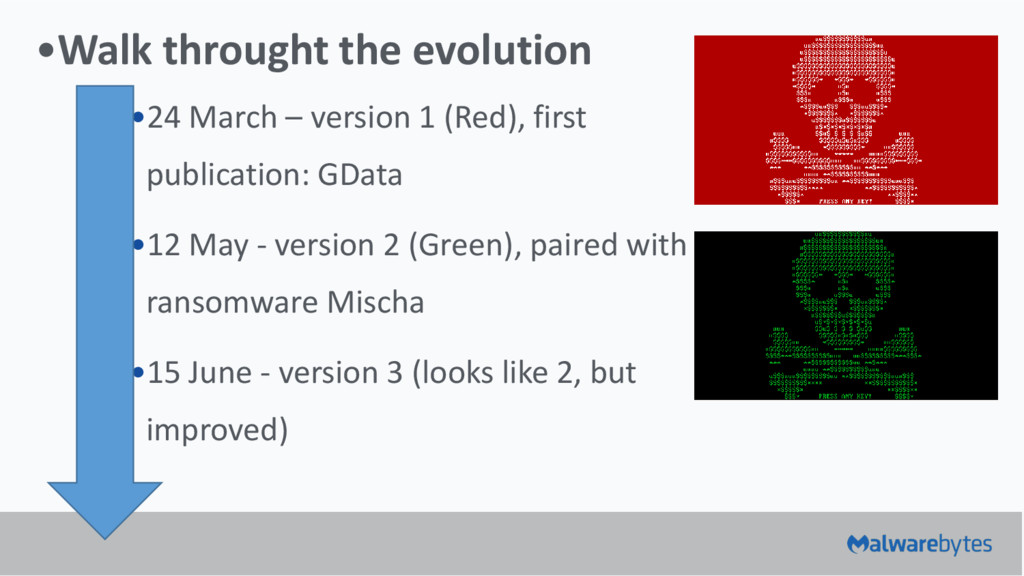
•Walk throught the evolution •24 March – version 1 (Red),
first publication: GData •12 May - version 2 (Green), paired with ransomware Mischa •15 June - version 3 (looks like 2, but improved) -
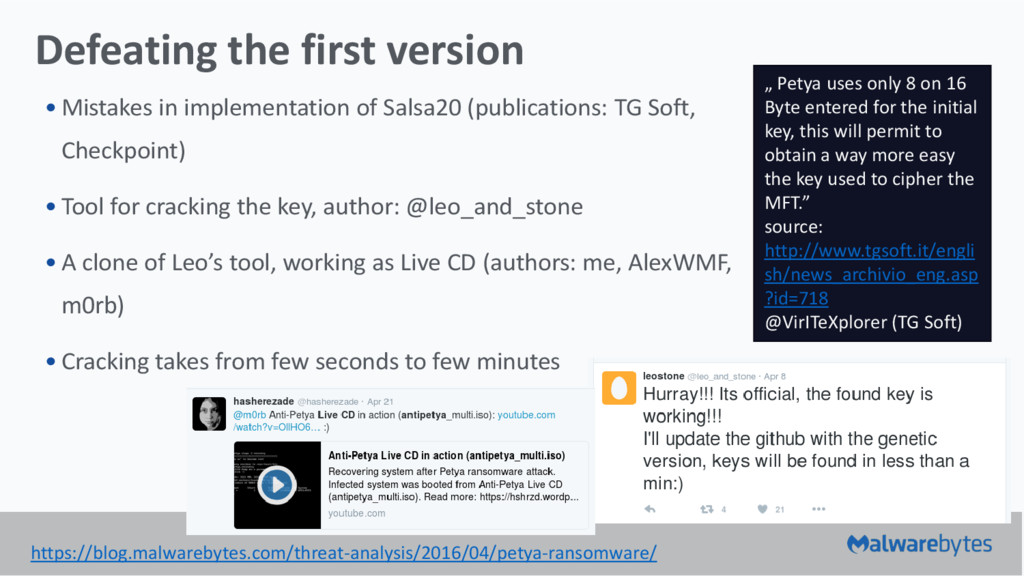
Defeating the first version •Mistakes in implementation of Salsa20 (publications:
TG Soft, Checkpoint) •Tool for cracking the key, author: @leo_and_stone •A clone of Leo’s tool, working as Live CD (authors: me, AlexWMF, m0rb) •Cracking takes from few seconds to few minutes „ Petya uses only 8 on 16 Byte entered for the initial key, this will permit to obtain a way more easy the key used to cipher the MFT.” source: http://www.tgsoft.it/engli sh/news_archivio_eng.asp ?id=718 @VirITeXplorer (TG Soft) https://blog.malwarebytes.com/threat-analysis/2016/04/petya-ransomware/ -
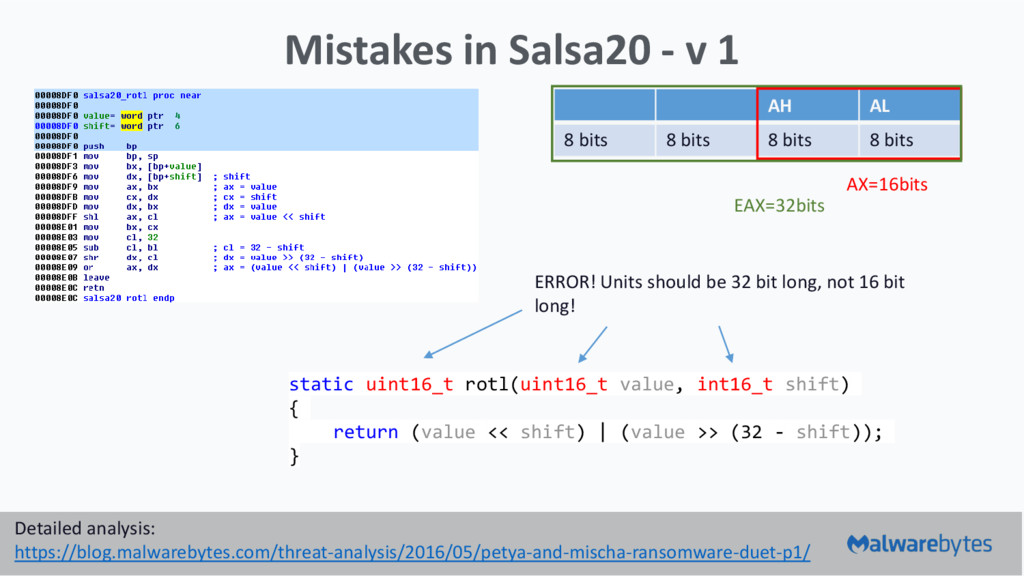
Mistakes in Salsa20 - v 1 Detailed analysis: https://blog.malwarebytes.com/threat-analysis/2016/05/petya-and-mischa-ransomware-duet-p1/ static
uint16_t rotl(uint16_t value, int16_t shift) { return (value << shift) | (value >> (32 - shift)); } ERROR! Units should be 32 bit long, not 16 bit long! AH AL 8 bits 8 bits 8 bits 8 bits AX=16bits EAX=32bits -
Mistakes in Salsa20 - v 1 Detailed analysis: https://blog.malwarebytes.com/threat-analysis/2016/05/petya-and-mischa-ransomware-duet-p1/ ERROR!
Units should be 32 bit long, not 16 bit long! void s20_hash(uint8_t seq[64]) { int i; uint16_t x[16]; uint16_t z[16]; for (i = 0; i < 16; ++i) x[i] = z[i] = s20_littleendian16(seq + (4 * i)); for (i = 0; i < 10; ++i) { s20_doubleround(z); } for (i = 0; i < 16; ++i) { z[i] += x[i]; s20_rev_littleendian_orig(seq + (4 * i), z[i]); } } -
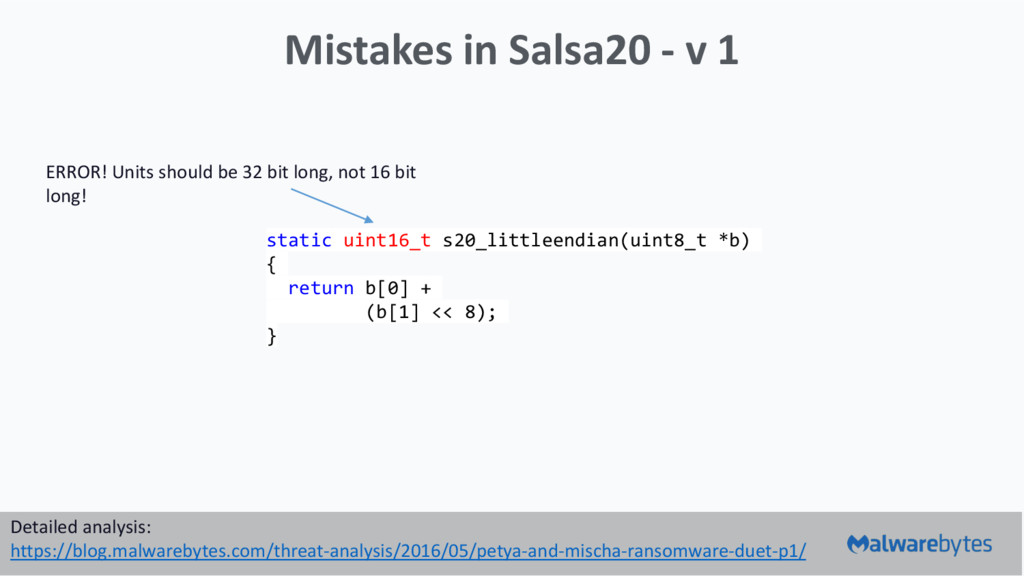
Mistakes in Salsa20 - v 1 Detailed analysis: https://blog.malwarebytes.com/threat-analysis/2016/05/petya-and-mischa-ransomware-duet-p1/ ERROR!
Units should be 32 bit long, not 16 bit long! static uint16_t s20_littleendian(uint8_t *b) { return b[0] + (b[1] << 8); } -
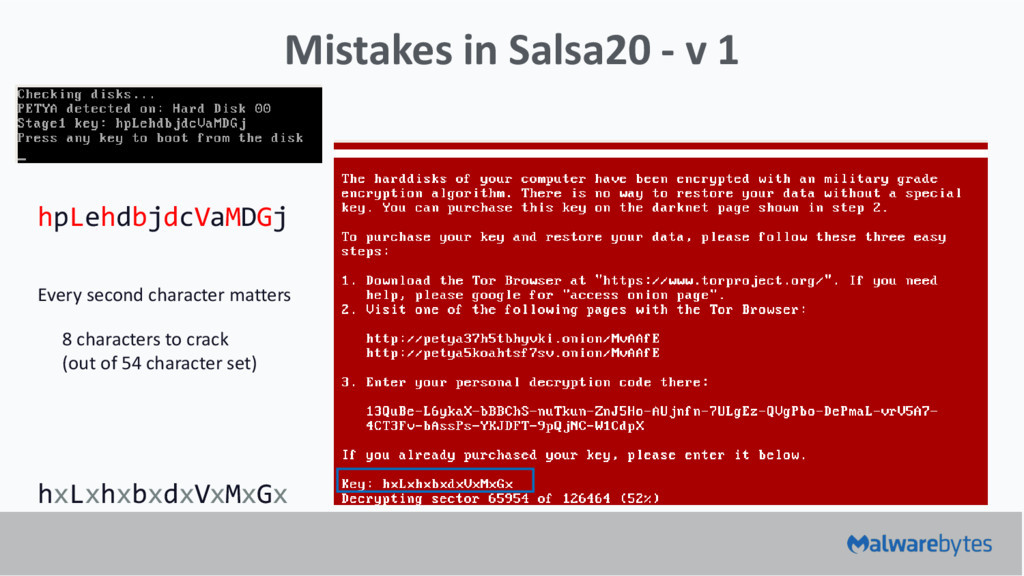
Mistakes in Salsa20 - v 1 hpLehdbjdcVaMDGj hxLxhxbxdxVxMxGx Every second
character matters 8 characters to crack (out of 54 character set) -
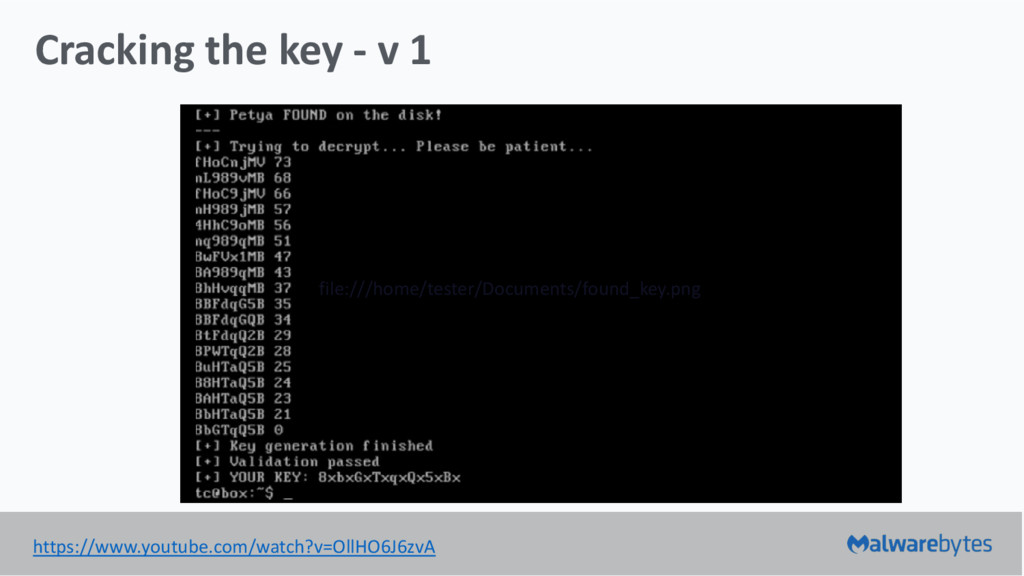
Cracking the key - v 1 •Brutforce possible, but... •Leo_and_Stone
found a better solution: genetic algorithms 54^8 = 72301961339136 vs 54^16 = 5.2275736134859E+27 Challenge: Find the key: 8 characters out of 54 character set -
Defeating the second version •Mistake in implementation of Salsa20 (found
by me) •GPU-based bruteforce decoder implemented by @procrash •Cracking takes about 3 days -
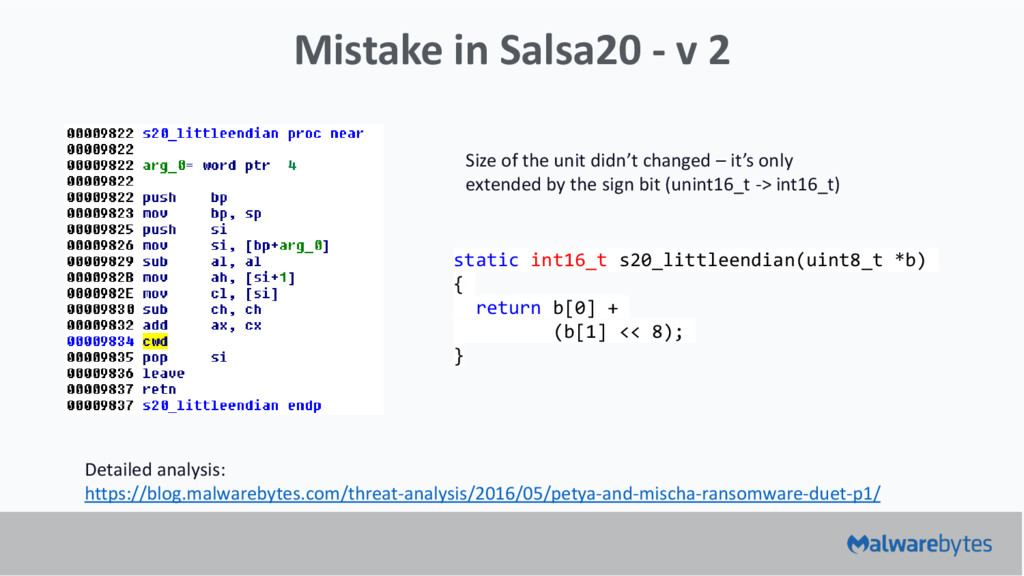
Mistake in Salsa20 - v 2 static int16_t s20_littleendian(uint8_t *b)
{ return b[0] + (b[1] << 8); } Detailed analysis: https://blog.malwarebytes.com/threat-analysis/2016/05/petya-and-mischa-ransomware-duet-p1/ Size of the unit didn’t changed – it’s only extended by the sign bit (unint16_t -> int16_t) -
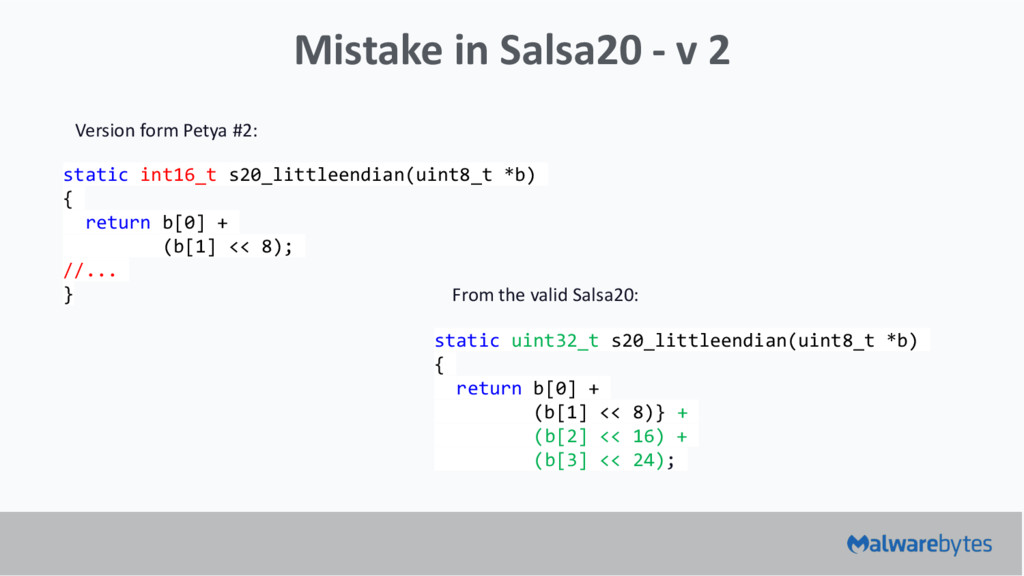
Mistake in Salsa20 - v 2 static int16_t s20_littleendian(uint8_t *b)
{ return b[0] + (b[1] << 8); //... } static uint32_t s20_littleendian(uint8_t *b) { return b[0] + (b[1] << 8)} + (b[2] << 16) + (b[3] << 24); Version form Petya #2: From the valid Salsa20: -
Mistake in Salsa20 - v 2 sHbGrSTkpCrhoKRt sHxxrSxxpCxxoKxx Every second
PAIR of characters matters 8 characters to crack (out of 54 character set) -
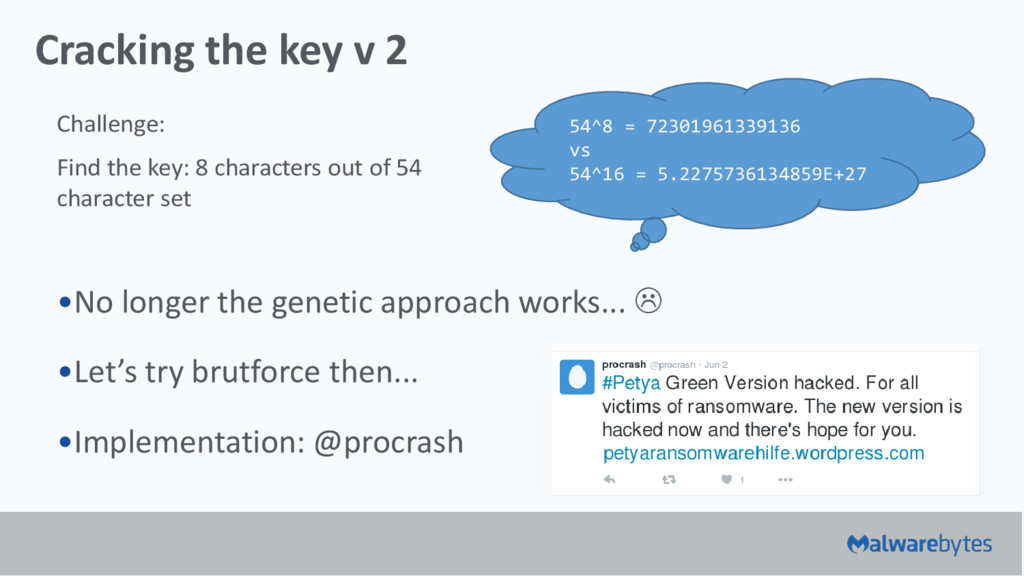
Cracking the key v 2 •No longer the genetic approach
works... •Let’s try brutforce then... •Implementation: @procrash 54^8 = 72301961339136 vs 54^16 = 5.2275736134859E+27 Challenge: Find the key: 8 characters out of 54 character set -
Status for today •The current version (3) uses valid Salsa20
• https://blog.malwarebytes.com/threat-analysis/2016/07/third-time-unlucky- improved-petya-is-out/ •Autor rents Petya to other criminals by an affiliate program •Recently deployed in Poland • https://www.cert.pl/news/single/kolejna-odslona-kampanii-komornika- sadowego-ransomware-petya-mischa/ -
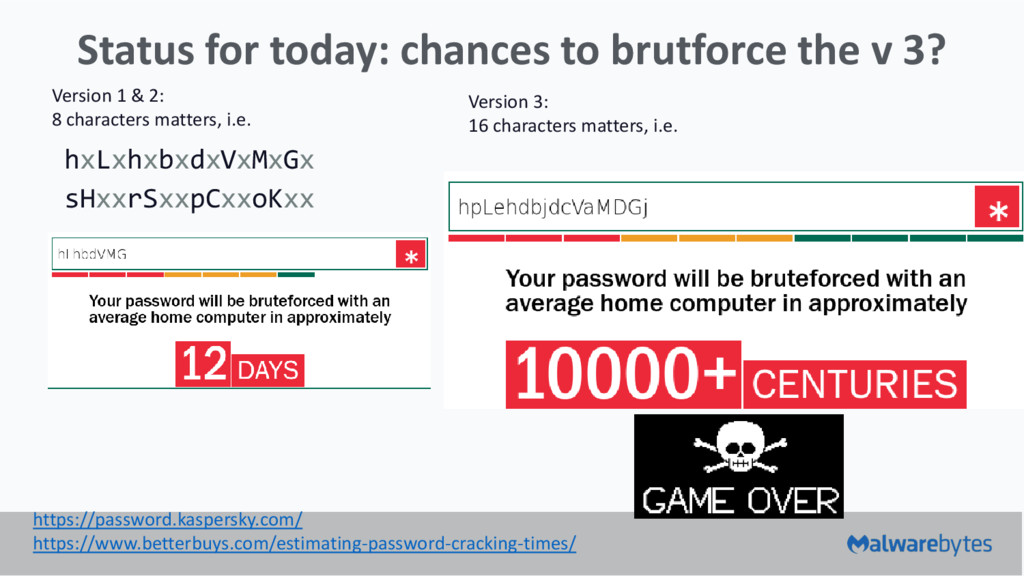
Status for today: chances to brutforce the v 3? Version
1 & 2: 8 characters matters, i.e. Version 3: 16 characters matters, i.e. hxLxhxbxdxVxMxGx sHxxrSxxpCxxoKxx https://password.kaspersky.com/ https://www.betterbuys.com/estimating-password-cracking-times/