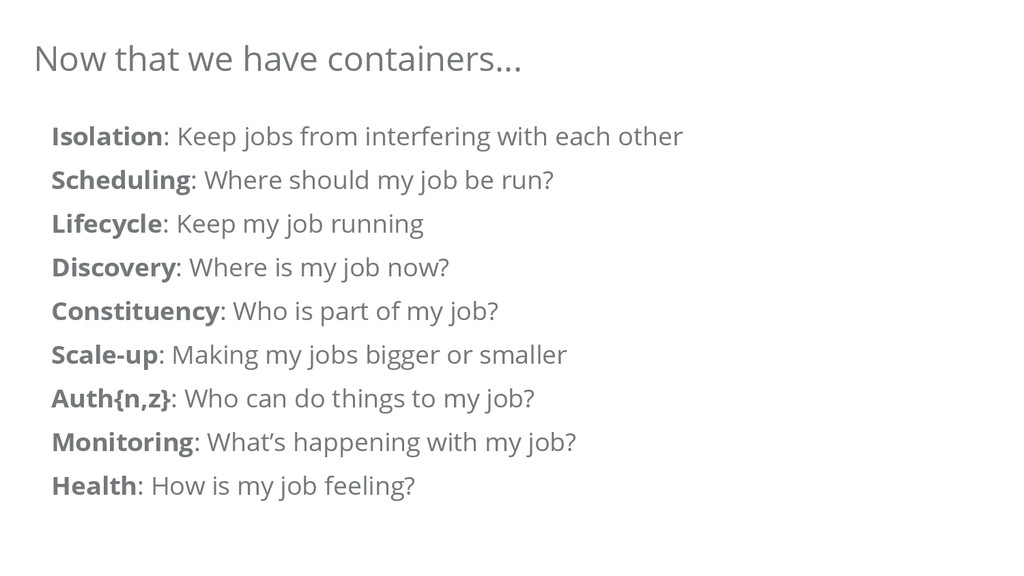
should my job be run? Lifecycle: Keep my job running Discovery: Where is my job now? Constituency: Who is part of my job? Scale-up: Making my jobs bigger or smaller Auth{n,z}: Who can do things to my job? Monitoring: What’s happening with my job? Health: How is my job feeling? Now that we have containers...
• Container orchestrator • Runs Docker containers • Supports multiple cloud and bare- metal environments • Inspired and informed by Google’s experiences and internal systems • Open source, written in Go Manage applications, not machines Kubernetes
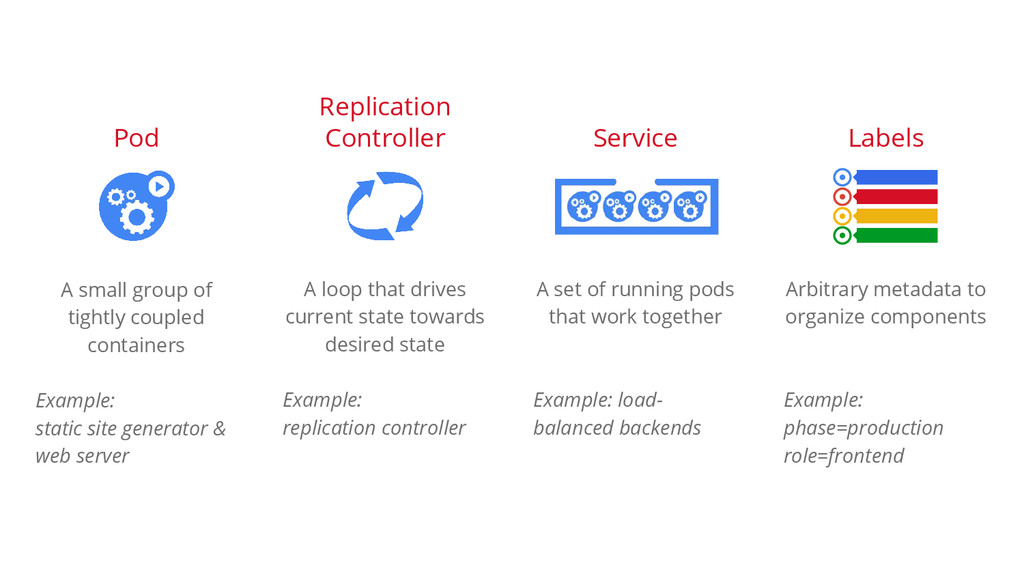
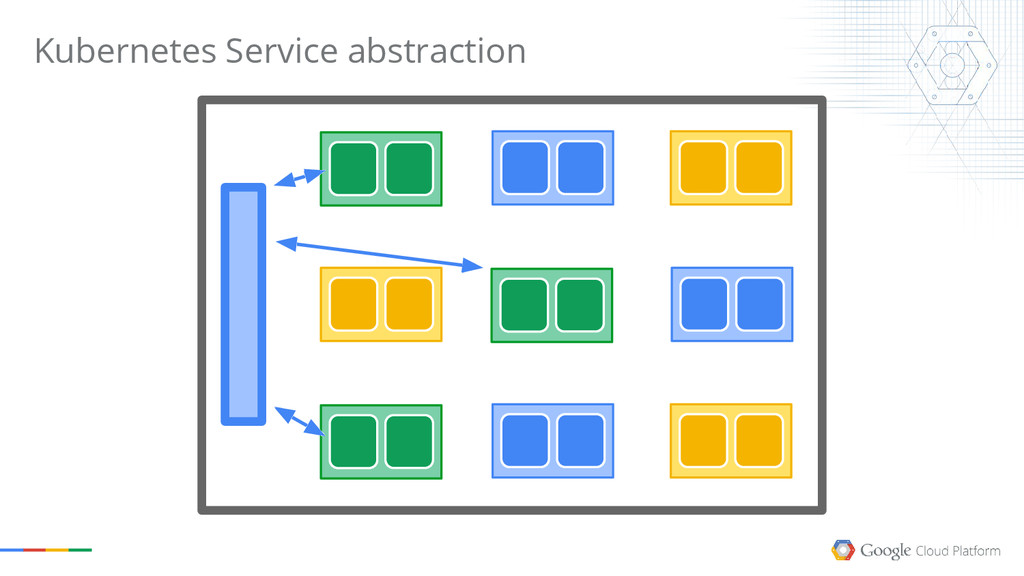
generator & web server A loop that drives current state towards desired state Example: replication controller A set of running pods that work together Example: load- balanced backends Arbitrary metadata to organize components Example: phase=production role=frontend Pod Replication Controller Service Labels
cgroups: Restrict resources a process can consume CPU, memory, disk IO, ... namespaces: Change a process’s view of the system Network interfaces, PIDs, users, mounts, ... capabilities: Limits what a user can do mount, kill, chown, etc They're processes! Containers
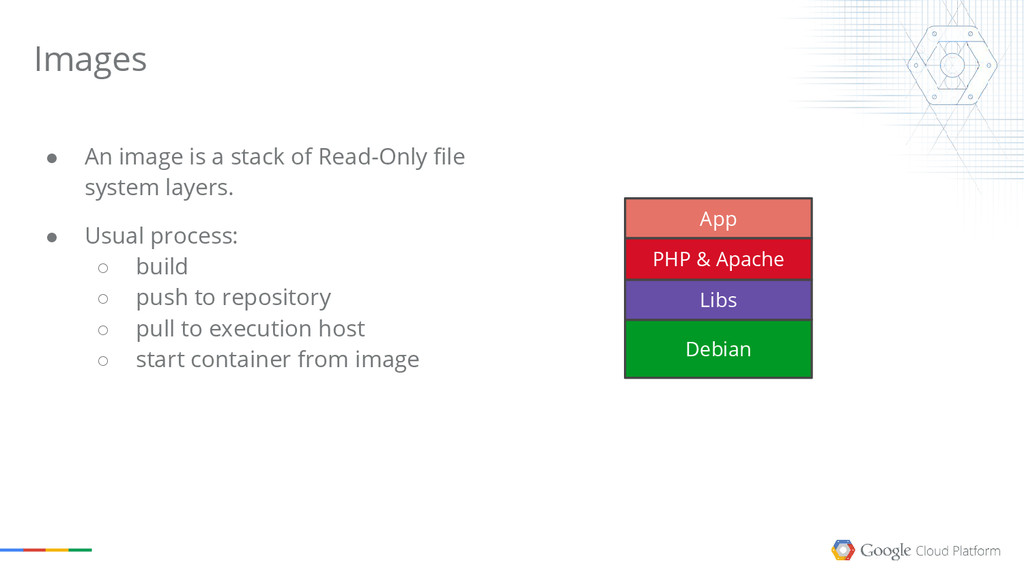
& Apache Libs Read / Write • A container is a process ◦ started with kernel restrictions ◦ a stack of shared Read-Only file system layers ◦ plus a process specific Read- Write layer • Every new container gets a new Read-Write layer. All containers from the same image start from exactly the same state!
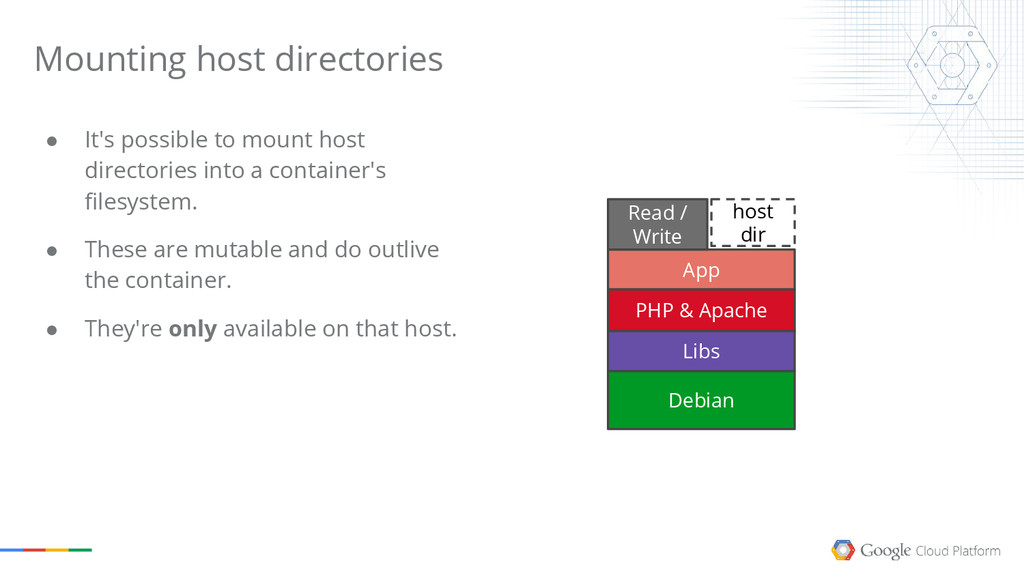
filesystem. • These are mutable and do outlive the container. • They're only available on that host. Mounting host directories Debian App PHP & Apache Libs Read / Write host dir
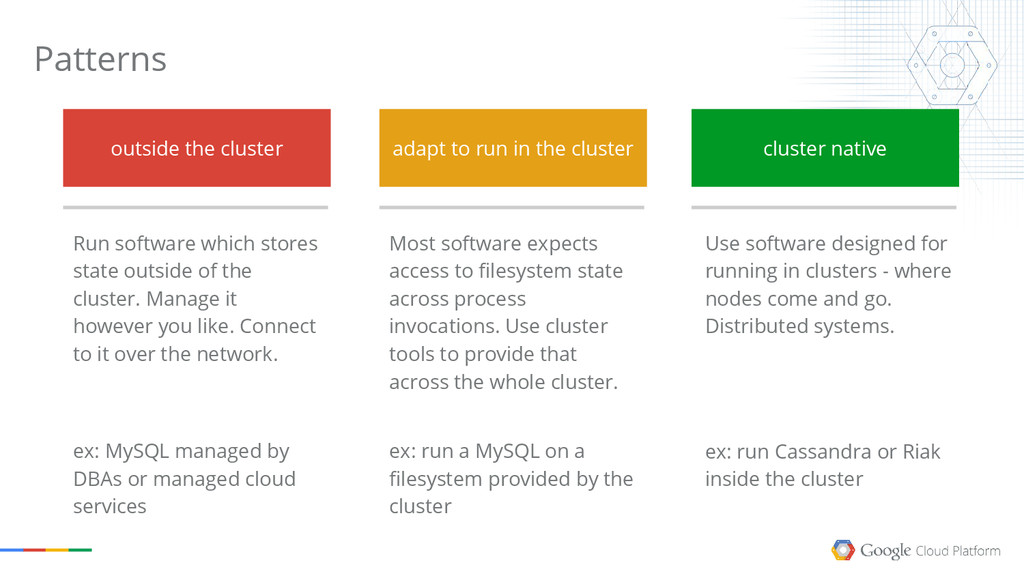
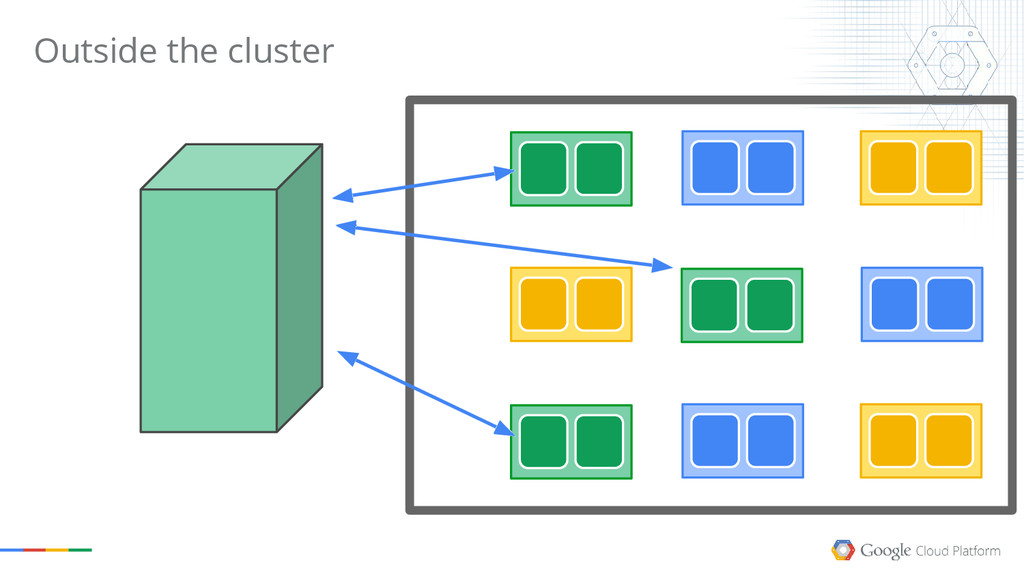
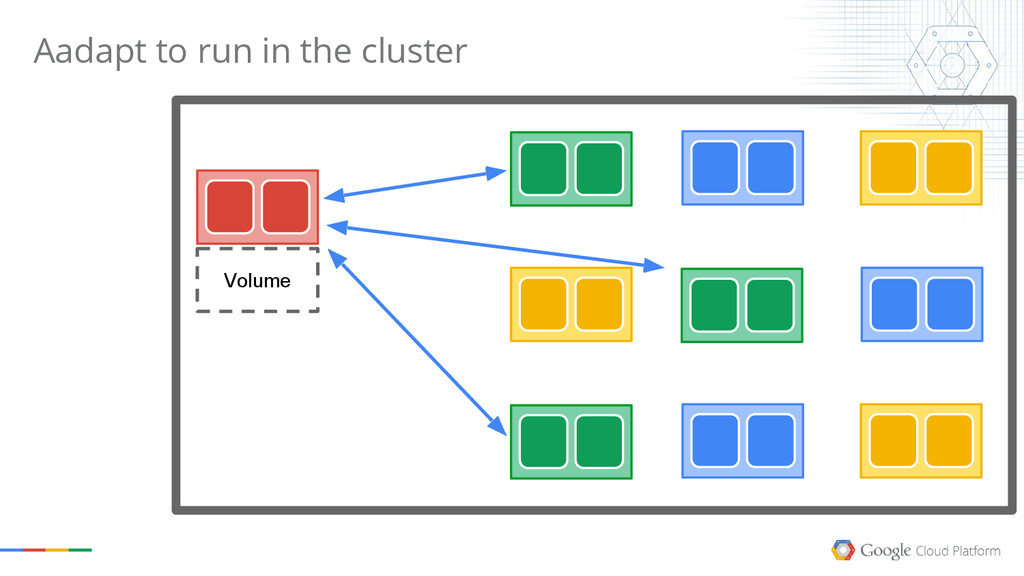
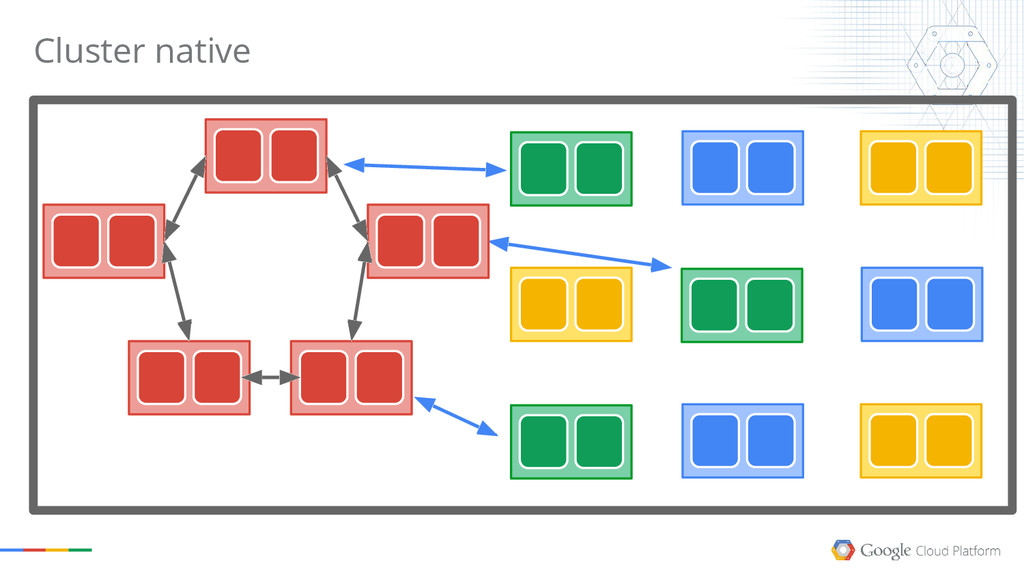
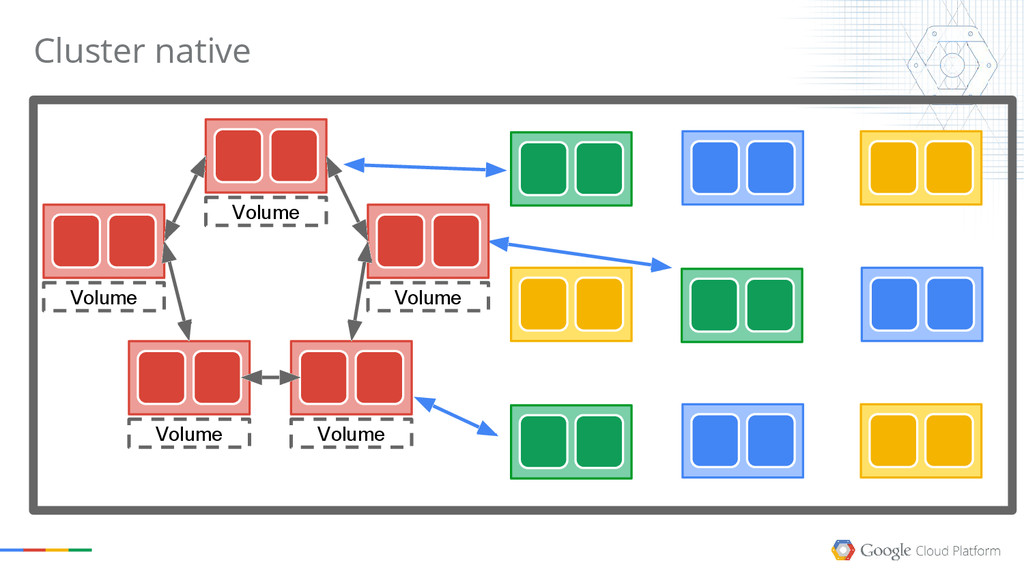
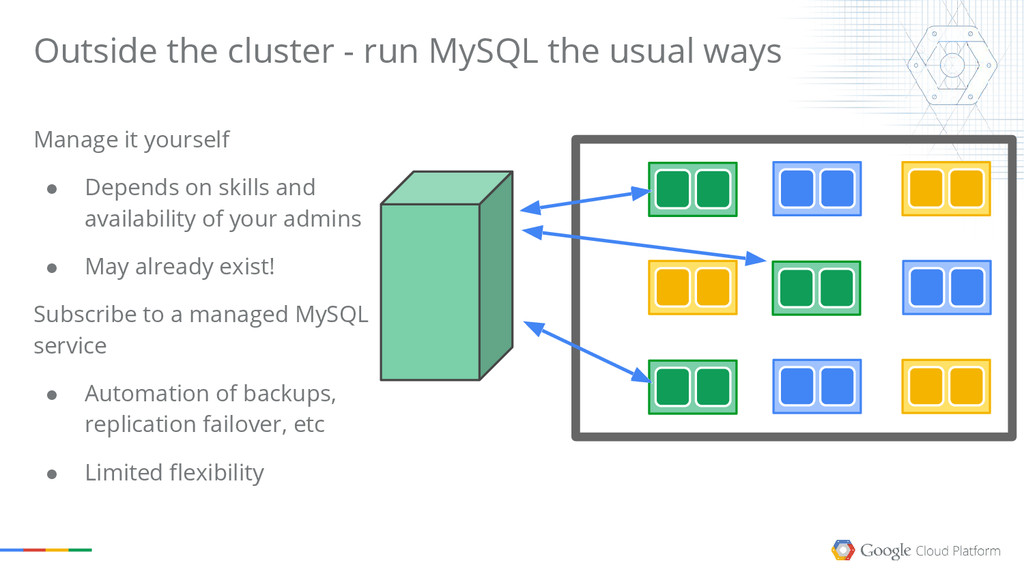
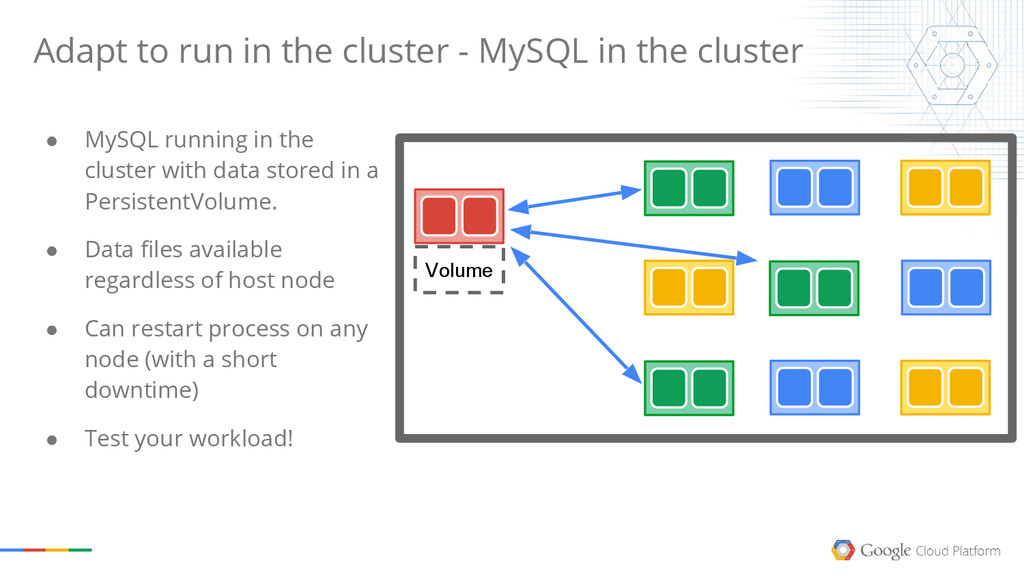
it however you like. Connect to it over the network. ex: MySQL managed by DBAs or managed cloud services Patterns Most software expects access to filesystem state across process invocations. Use cluster tools to provide that across the whole cluster. ex: run a MySQL on a filesystem provided by the cluster outside the cluster adapt to run in the cluster cluster native Use software designed for running in clusters - where nodes come and go. Distributed systems. ex: run Cassandra or Riak inside the cluster
it yourself • Depends on skills and availability of your admins • May already exist! Subscribe to a managed MySQL service • Automation of backups, replication failover, etc • Limited flexibility
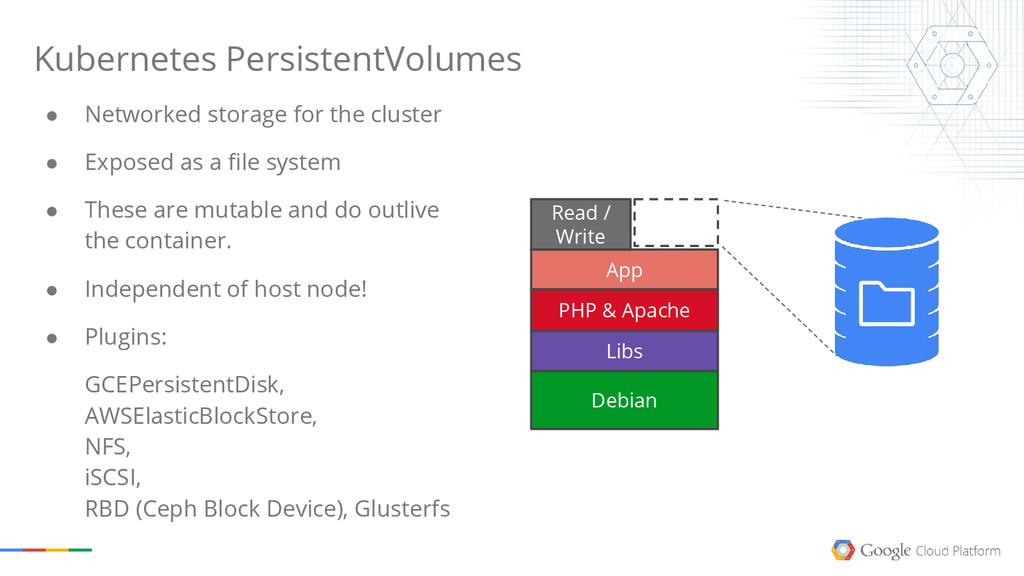
cluster Volume • MySQL running in the cluster with data stored in a PersistentVolume. • Data files available regardless of host node • Can restart process on any node (with a short downtime) • Test your workload!
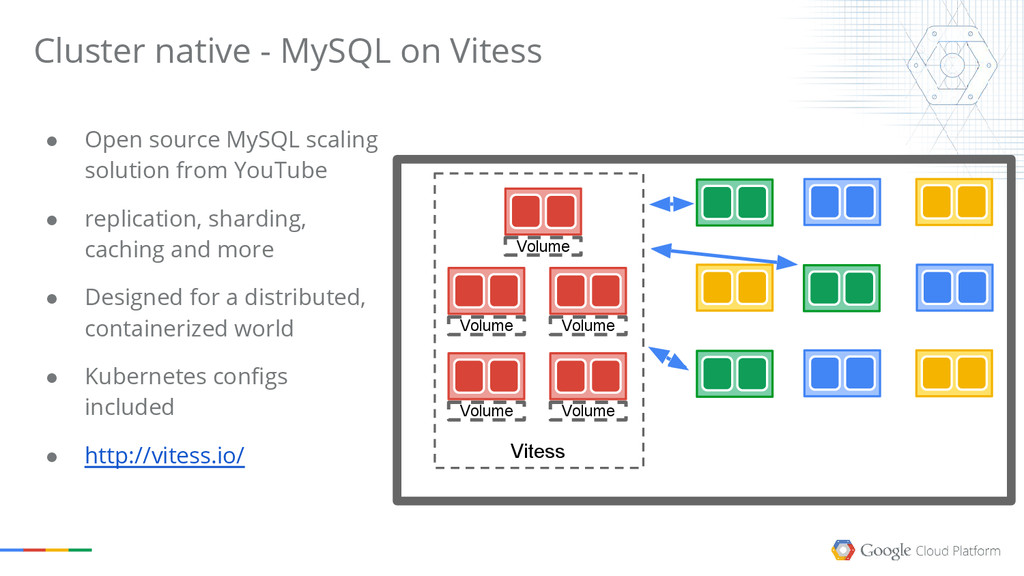
scaling solution from YouTube • replication, sharding, caching and more • Designed for a distributed, containerized world • Kubernetes configs included • http://vitess.io/ Volume Volume Volume Volume Volume Vitess
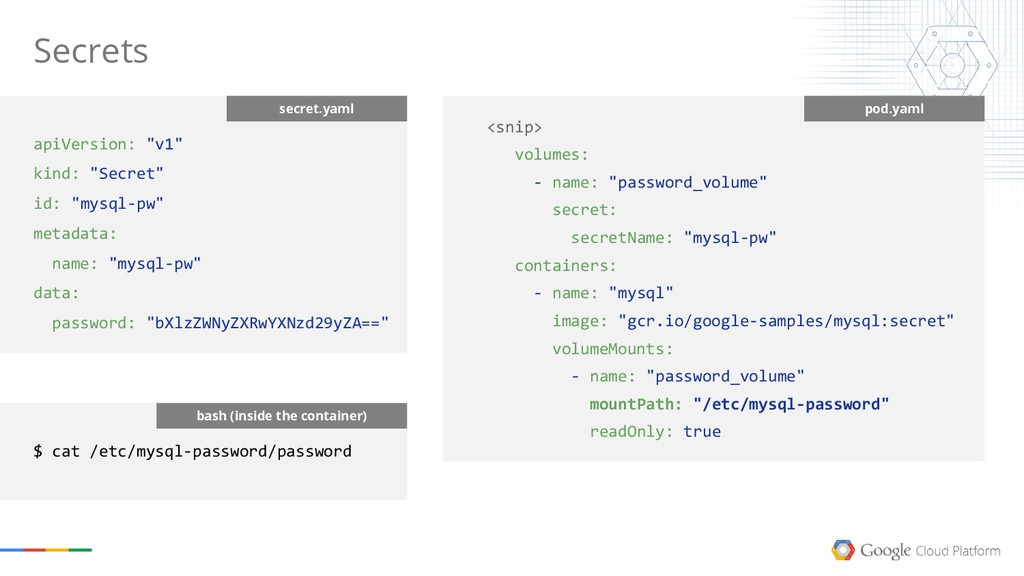
at Google with Borg • http://research.google.com/pubs/pub43438.html Kubernetes: http://kubernetes.io Try Kubernetes quickly and easily on Google Container Engine • https://cloud.google.com/container-engine/ Try these patterns in Kubernetes • https://github.com/GoogleCloudPlatform/kubernetes/blob/master/docs/services. md#services-without-selectors • https://github.com/GoogleCloudPlatform/kubernetes/tree/master/examples/mysql- wordpress-pd • https://github.com/GoogleCloudPlatform/kubernetes/tree/master/examples/cassandra • https://github.com/GoogleCloudPlatform/kubernetes/blob/master/docs/secrets.md • https://vitess.io/ Next steps (take a photo)


 ianlewis
 sue445
 kaminashi
 inesmontani
 minorun365
 legalontechnologies
 oidfj
 timakin
 nicholsjasper
 atalie2m
 amarelo_n24
 ginjihayashi
 shotashiratori
 tmiket
 konakalab
 aleyda
 sergeychernyshev
 katarinadahlin
 destraynor
 akihiro_kokubo
 reverentgeek
 sabderemane
 joshbly
 addyosmani
 bkeepers