Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Integrating security into an existing agile SDLC
Search
Laura Bell
September 12, 2014
Technology
170
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Integrating security into an existing agile SDLC
Laura Bell
September 12, 2014
More Decks by Laura Bell
See All by Laura Bell
DIY security for the amateur superhero
ladynerd
0
320
Hackcon 11 - Protecting our people
ladynerd
0
260
Security in a container based world
ladynerd
0
170
Securing Microservice Architectures
ladynerd
2
380
Better Connected
ladynerd
0
92
Continuous Security
ladynerd
3
1.2k
Automated Human Vulnerability Scanning with AVA
ladynerd
3
2.8k
Blindsided by security
ladynerd
0
150
Practical tools for privacy audit
ladynerd
0
240
Other Decks in Technology
See All in Technology
HacobuにおけるFDEとは/登壇資料(戸井田 裕貴)
hacobu
PRO
1
670
カンファレンスに参加した後の浮遊感とセルフケア
pauli
0
270
Mastering Agentic Development: Harness Engineering for Effective Coding Agents
konippi
3
670
Claude Designがめちゃくちゃ便利なので使ってほしい
diggymo
0
180
HolmesGPTで始めるSREエージェント入門!プラットフォームの障害調査はAIにお任せ 〜
leveragestech
PRO
0
130
【Findyテック文化祭ワークショップ】新卒エンジニア&採用担当と作る、 なりたい姿と今やるべき一歩
dip_tech
PRO
0
150
KanaAI
shreyas1009
0
140
高負荷プロダクション環境におけるAWS Lambdaのリアル 〜スケールとコストを左右する実行ライフサイクルの技術仕様〜
maimyyym
2
840
CI/CDではもう遅い - 人とAIが迂回しないDevSecOps Verify基盤の再設計 -
kintotechdev
1
580
Confitura 2026
logico_jp
0
120
20260929_AmazonGuardDutyの検出通知メールにAWS DevOpsAgentの調査結果を追加する
yhana
1
400
個別開発で終わらせない。 現場の課題をプロダクトの強さに変える StockmarkのFDE
ktkrhr
0
510
Featured
See All Featured
Visual Storytelling: How to be a Superhuman Communicator
reverentgeek
2
690
The SEO identity crisis: Don't let AI make you average
varn
0
570
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.3k
The Straight Up "How To Draw Better" Workshop
denniskardys
239
140k
The State of eCommerce SEO: How to Win in Today's Products SERPs - #SEOweek
aleyda
2
12k
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
The Cost Of JavaScript in 2023
addyosmani
55
10k
Discover your Explorer Soul
emna__ayadi
2
1.3k
The Web Performance Landscape in 2024 [PerfNow 2024]
tammyeverts
12
1.3k
Typedesign – Prime Four
hannesfritz
42
3.2k
Leveraging Curiosity to Care for An Aging Population
cassininazir
1
520
Transcript
ARC208
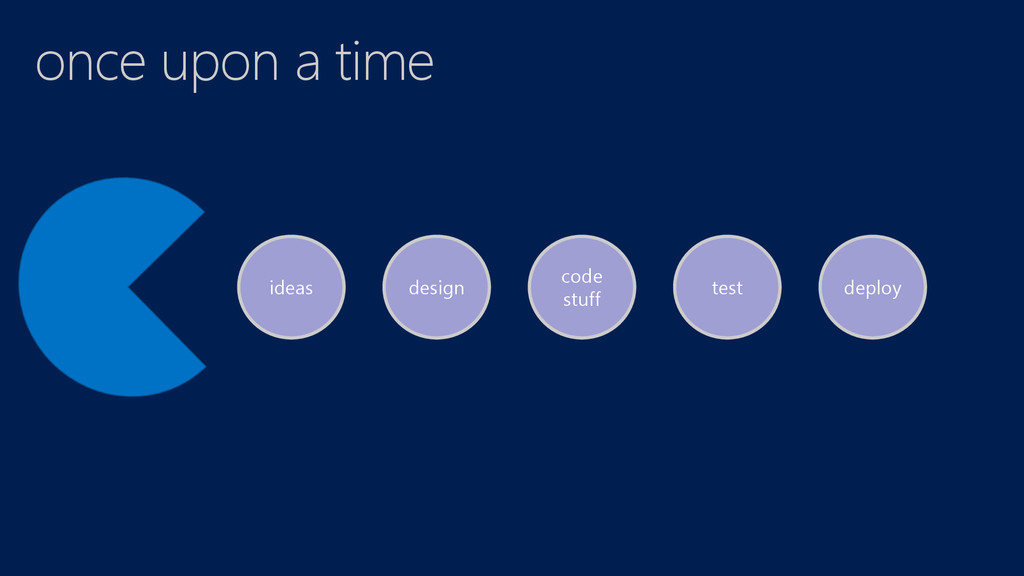
once upon a time design code stuff ideas test deploy
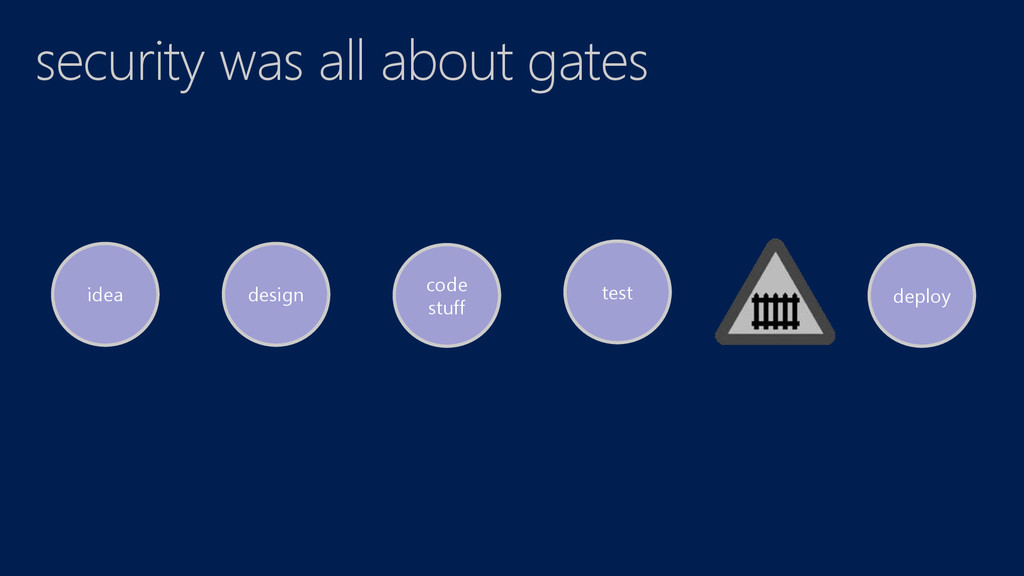
security was all about gates design code stuff idea test
deploy
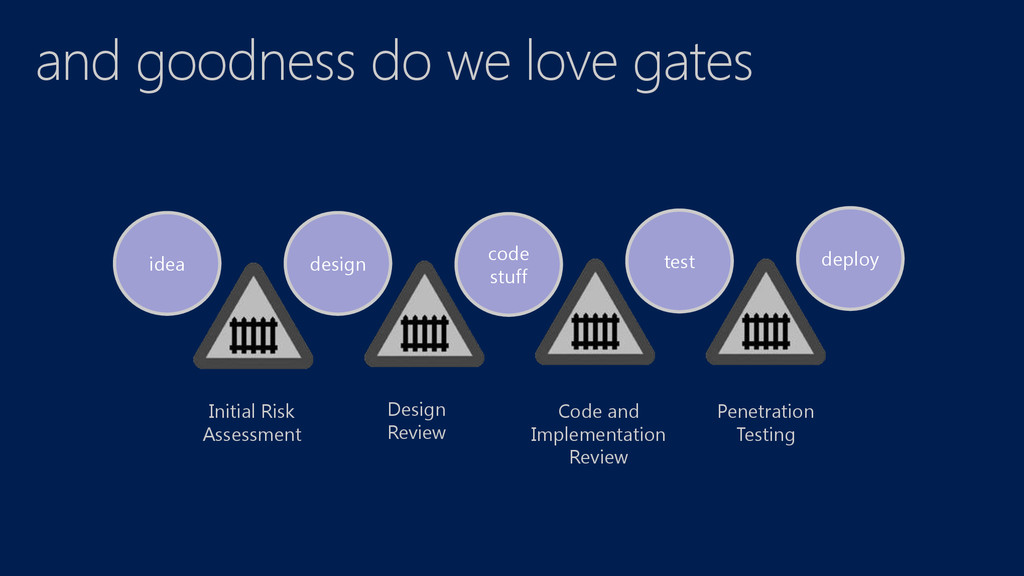
and goodness do we love gates design code stuff idea
test deploy Initial Risk Assessment Design Review Code and Implementation Review Penetration Testing
same thing, just more frequently?
None
Why don’t you do security?
we can make you look good Proactive security engagement increases:
Preparedness Credibility Market awareness Strategic thinking
So what does agile security need to be 1. Able
to empower developers 2. Cost effective 3. Pragmatic and flexible 4. Easy to integrate with existing workflows 5. Scalable
common misconceptions
avoidance != management
too little to fail (at security)
the sky is not always falling* *except when it is
(then you should really do something about it)
agility increases risk
Ten steps to a better, stronger and more secure you
regardless of budget, organisation size or how cool you are
1. know your stack Languages Libraries Operating Systems Applications Third
Party Services
2. learn to add, adapt and abandon
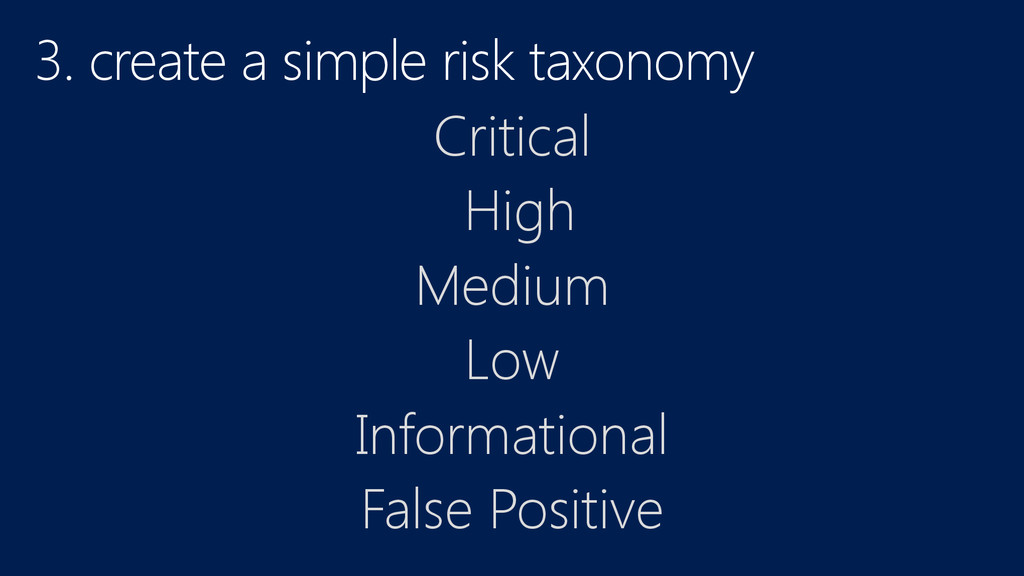
3. create a simple risk taxonomy Critical High Medium Low
Informational False Positive
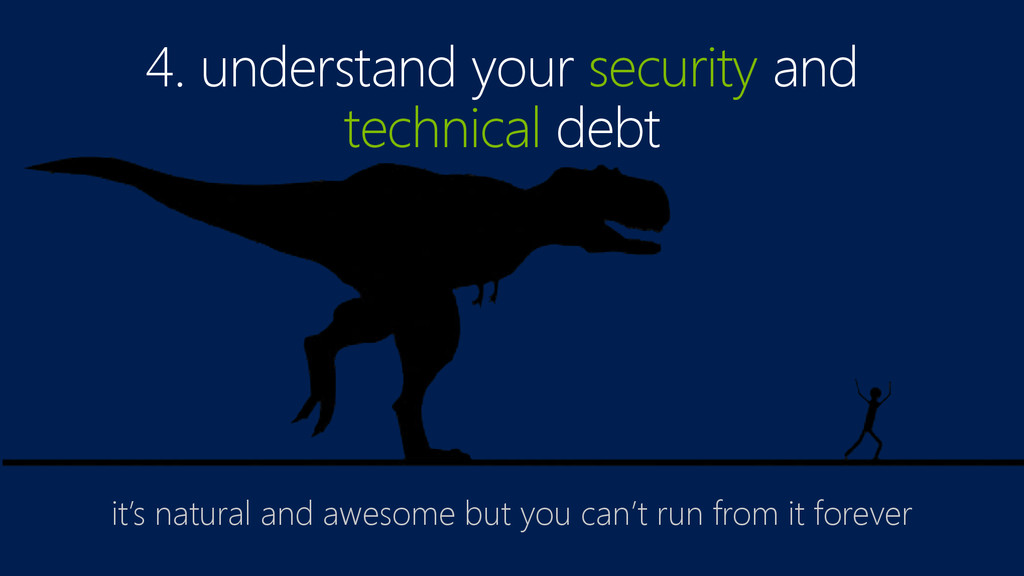
4. understand your security and technical debt it’s natural and
awesome but you can’t run from it forever
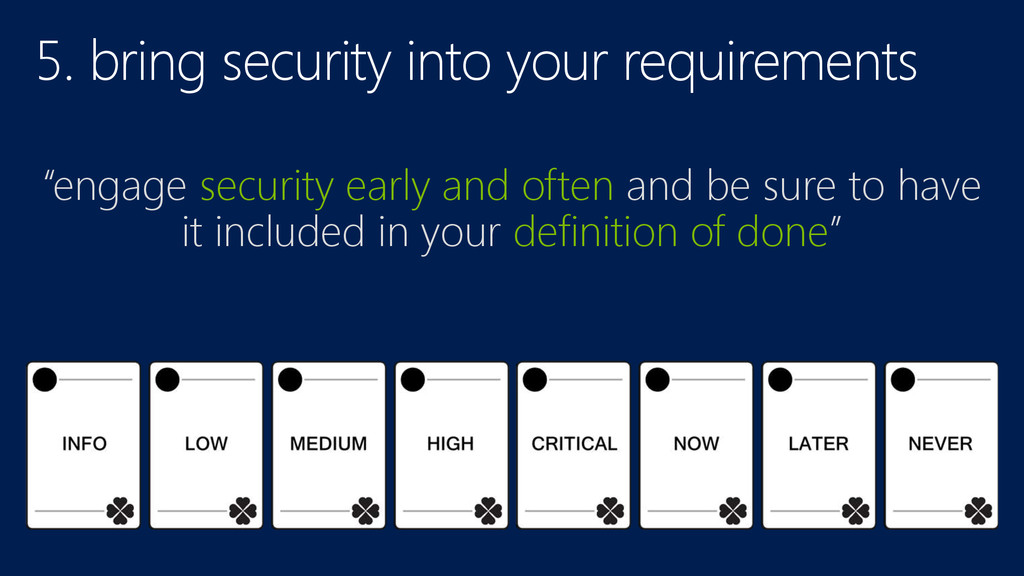
5. bring security into your requirements “engage security early and
often and be sure to have it included in your definition of done”
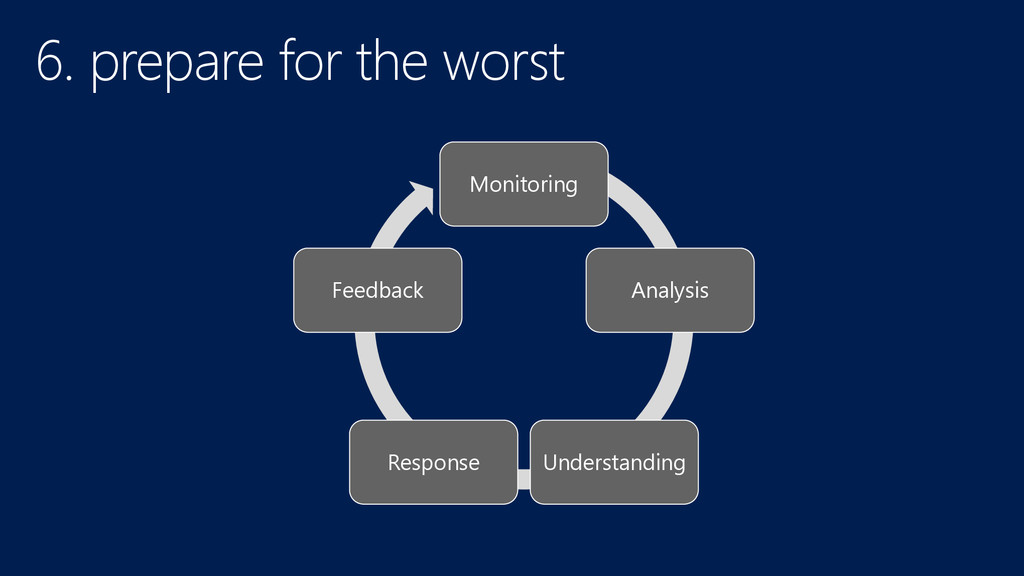
6. prepare for the worst Monitoring Analysis Understanding Response Feedback
7. build an empire one developer at a time
8. design your workflows “the best technical people I know
work really hard to make themselves redundant. “
fails
10. outsource smartly “if you are going to spend the
money, research your options, scope well and be demanding”
common challenges and how to conquer, obliterate or otherwise win
compliance is a priority “nothing is more fatal to a
new business than the fines for non-compliance”
maintain momentum “more secure today than yesterday”
use your words No Simple way to remove risk Must
be logically applied and justified Does not remove the original need or objective Yes Scary for security people Accepts risks and understands them Enables innovation Encourage safe usage
None
Ready to get started? …take a deep breath
None
None


 ladynerd
 hacobu
 pauli
 konippi
 diggymo
 leveragestech
 dip_tech
 shreyas1009
 maimyyym
 kintotechdev
 logico_jp
 yhana
 ktkrhr
 reverentgeek
 varn
 tomoyanonymous
 denniskardys
 aleyda
 garrettdimon
 eileencodes
 addyosmani
 emna__ayadi
 tammyeverts
 hannesfritz
 cassininazir