Share
Embed
Seamless device migration using LINE secure backups
Charles Hubain
LINE Security Development Team Senior Security Engineer
https://linedevday.linecorp.com/jp/2019/sessions/F1-2
LINE DevDay 2019
November 20, 2019
Transcript
34 slides
-
2019 DevDay Seamless Device Migration Using LINE Secure Backups >
Charles Hubain > LINE Security Development Team Senior Security Engineer -
> Breaking white-box cryptographic implementation see SideChannelMarvels project on Github
& relevant papers > Writing reverse engineering tools see QBDI on Github > Used to work as a security consultant in Paris software, cryptography, hardware security audits & certifications Who Am I? -
> Breaking implementations is much easier than building secure ones
> Breaking has a short term impact, building has a long term impact > During my first internship I was told I should stop breaking stuff … and try building secure things instead Breaking vs Building -
> In practice, development team: > misunderstands security specifications >
lacks time > makes security mistakes > Ideally, security team: > proposes security specifications to development team > audits resulting implementations Security in a Big Company -
> Provide them as modules and micro-services => straightforward integration
> Integrated inside security department => better communication with other security teams > Design and develop security features => relieve development team workload Security Development Team -
> Letter Sealing (E2EE) key backup => This talk >
Supporting LINE banking projects > FIDO2 password-less authentication => Shin Ki-Eun talk Our Projects -
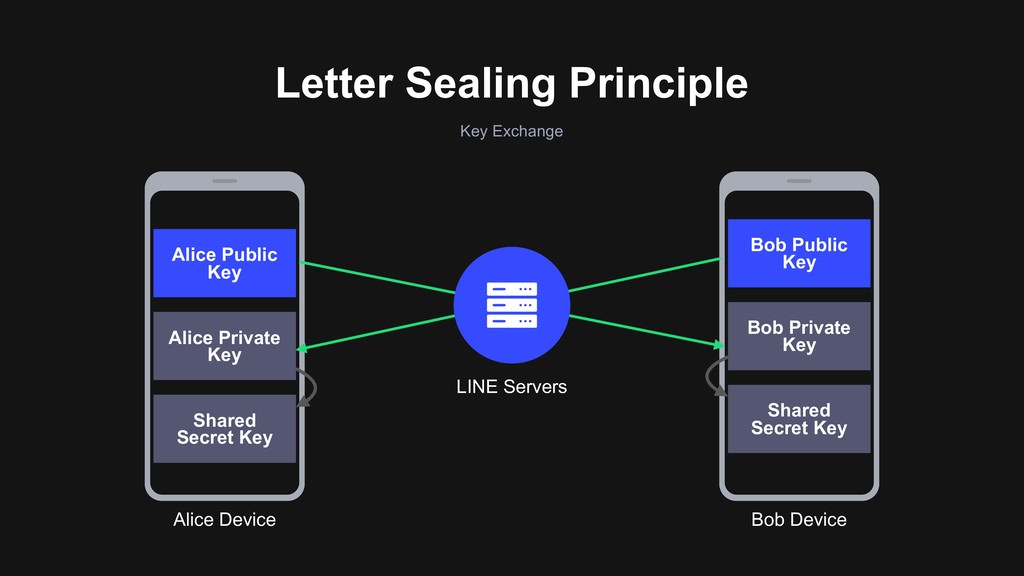
Alice Private Key Alice Public Key Shared Secret Key Letter
Sealing Principle Key Exchange LINE Servers Alice Device Bob Device Bob Private Key Bob Public Key Shared Secret Key -
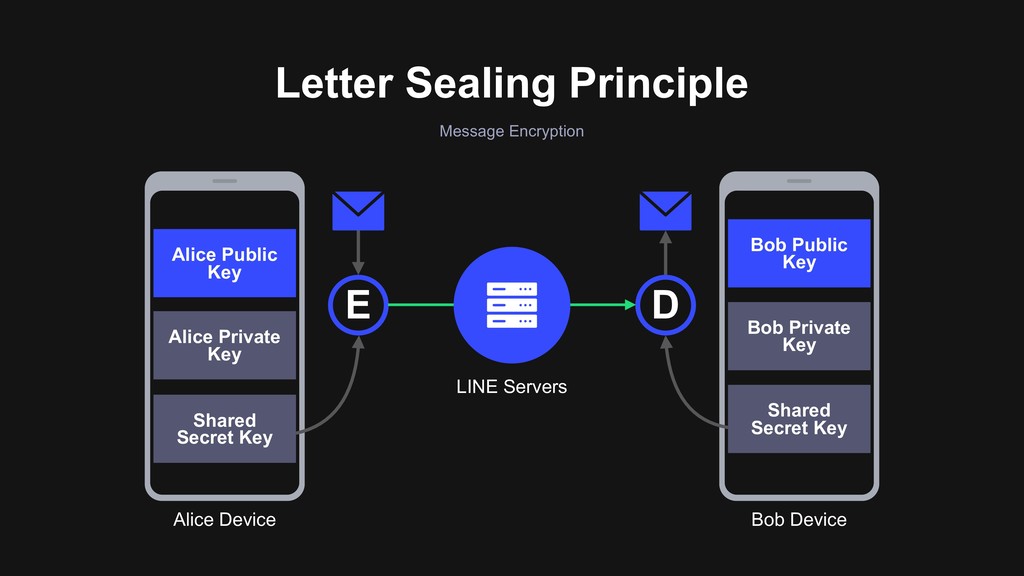
Letter Sealing Principle Message Encryption LINE Servers Alice Device Bob
Device E D Alice Private Key Alice Public Key Shared Secret Key Bob Private Key Bob Public Key Shared Secret Key -
Properties > Server only store encrypted messages For more details
please read the Letter Sealing white paper available online > Server and network only see devices public key Letter Sealing Principle > Message is end-to-end encrypted with a shared secret key only known by the devices -
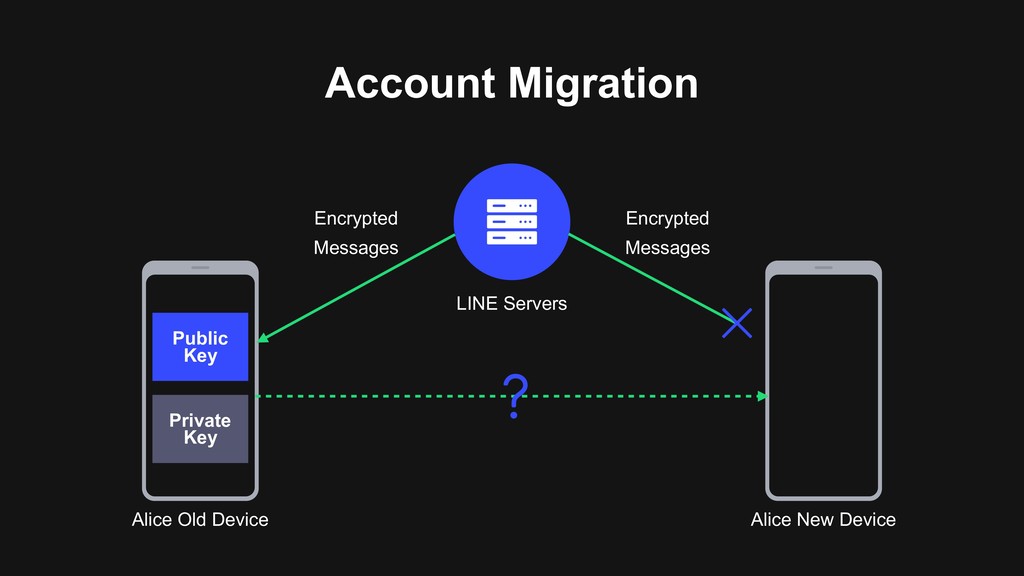
Account Migration LINE Servers Alice Old Device Alice New Device
Private Key Public Key Encrypted Messages Encrypted Messages -
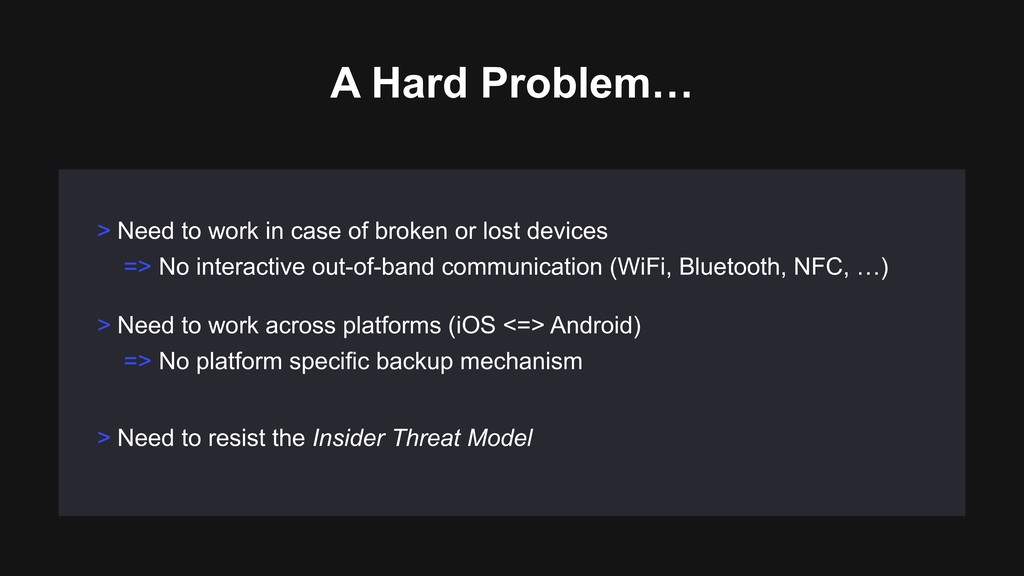
> Need to work across platforms (iOS <=> Android) =>
No platform specific backup mechanism > Need to resist the Insider Threat Model > Need to work in case of broken or lost devices => No interactive out-of-band communication (WiFi, Bluetooth, NFC, …) A Hard Problem… -
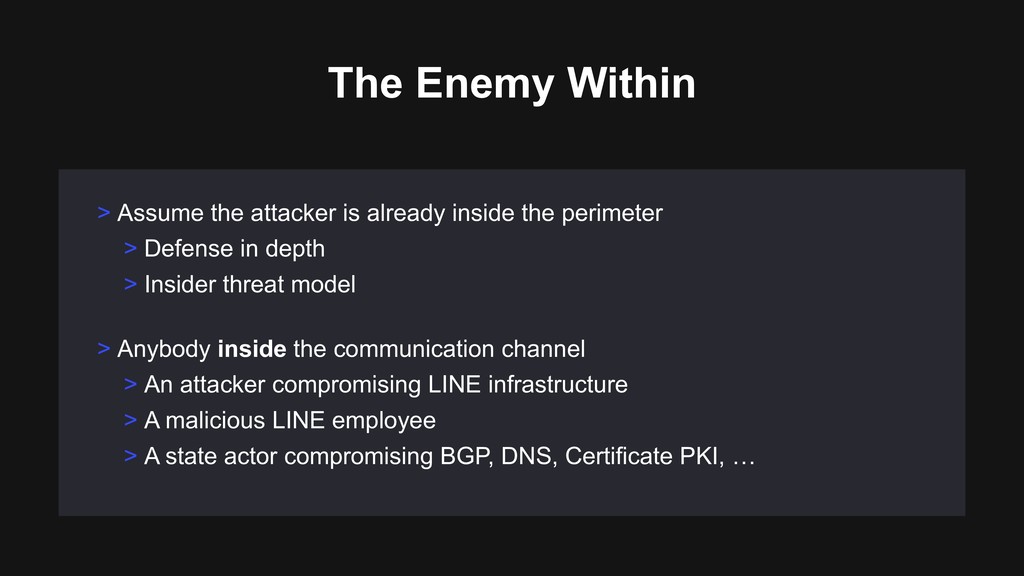
> Assume the attacker is already inside the perimeter >
Defense in depth > Insider threat model > Anybody inside the communication channel > An attacker compromising LINE infrastructure > A malicious LINE employee > A state actor compromising BGP, DNS, Certificate PKI, … The Enemy Within -
The Best UX… LINE Servers Alice Old Device Alice New
Device Private Key Public Key Encrypted Messages Encrypted Messages But the Worst Security Private Key Private Key -
But the Worst Security - Anybody inside the perimeter sees
the private key, completely compromising the letter sealing - The security level is equivalent to no encryption +No interaction required by the user The Best UX… -
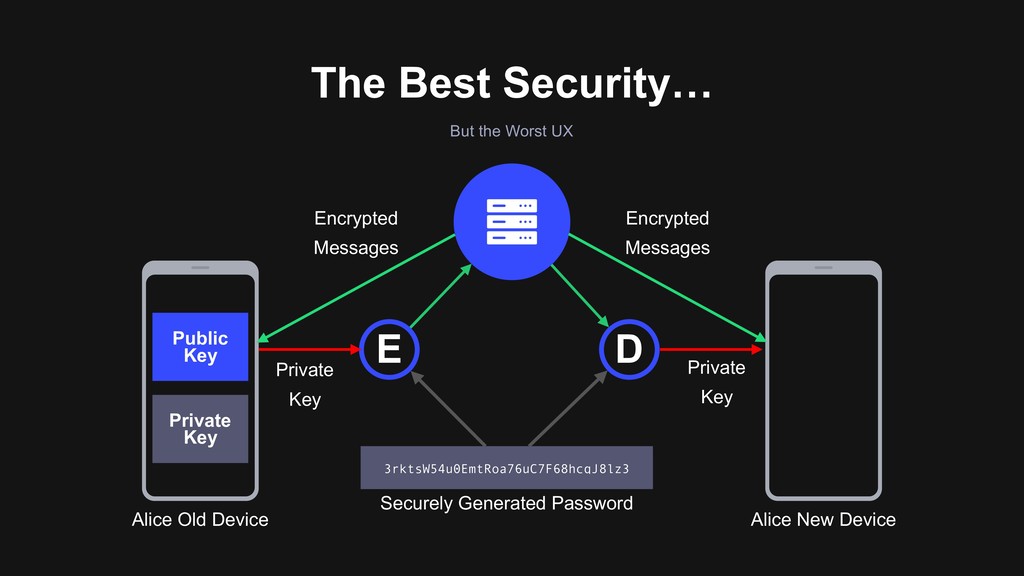
The Best Security… Alice Old Device Alice New Device Private
Key Public Key Encrypted Messages Encrypted Messages But the Worst UX Private Key Private Key E D 3rktsW54u0EmtRoa76uC7F68hcqJ8lz3 Securely Generated Password -
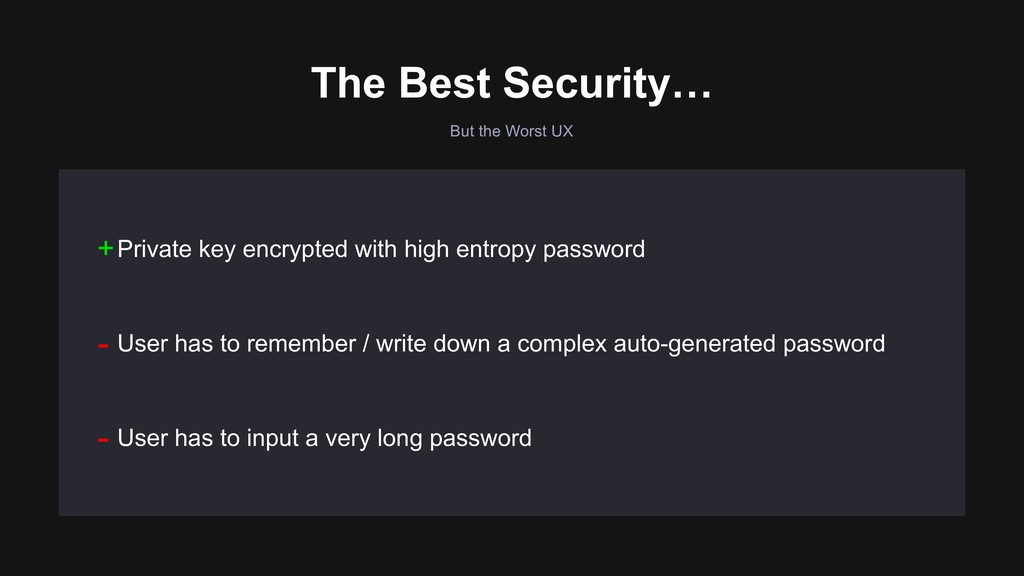
- User has to remember / write down a complex
auto-generated password - User has to input a very long password +Private key encrypted with high entropy password The Best Security… But the Worst UX -
Inverse Heat Death > Key backups could be decrypted using
offline brute-force > Users are bad at choosing and remembering complex (high entropy) passwords > Simple (low entropy) passwords are easy to enumerate 6 digits PIN code => 1 000 000 possibilities 25 most common passwords cover 10% of passwords in usage¹ Danger of Low Entropy ¹ https://time.com/4639791/worst-passwords-2016/ -
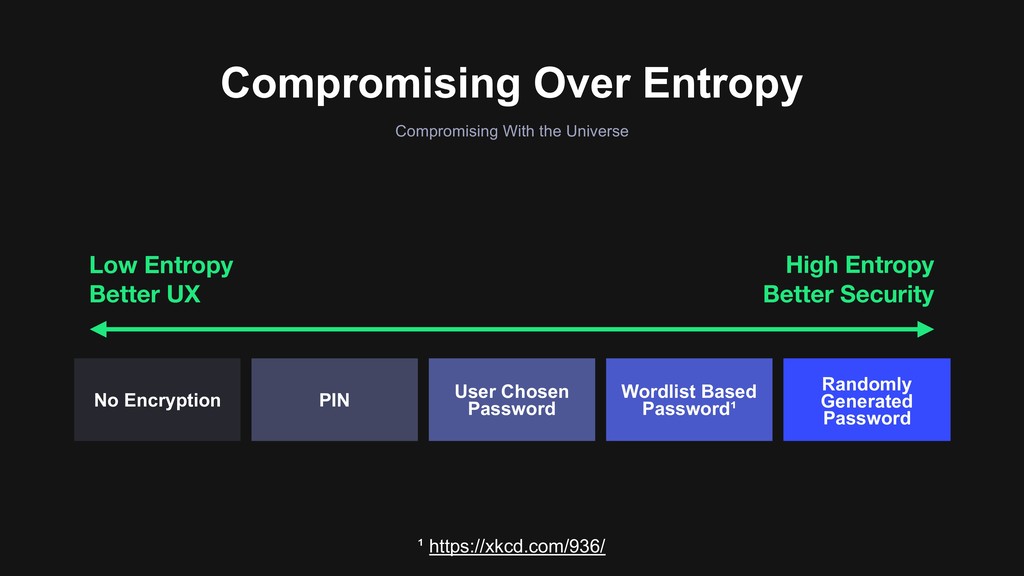
Compromising Over Entropy Compromising With the Universe High Entropy Better
Security Low Entropy Better UX No Encryption PIN User Chosen Password Wordlist Based Password¹ Randomly Generated Password ¹ https://xkcd.com/936/ -
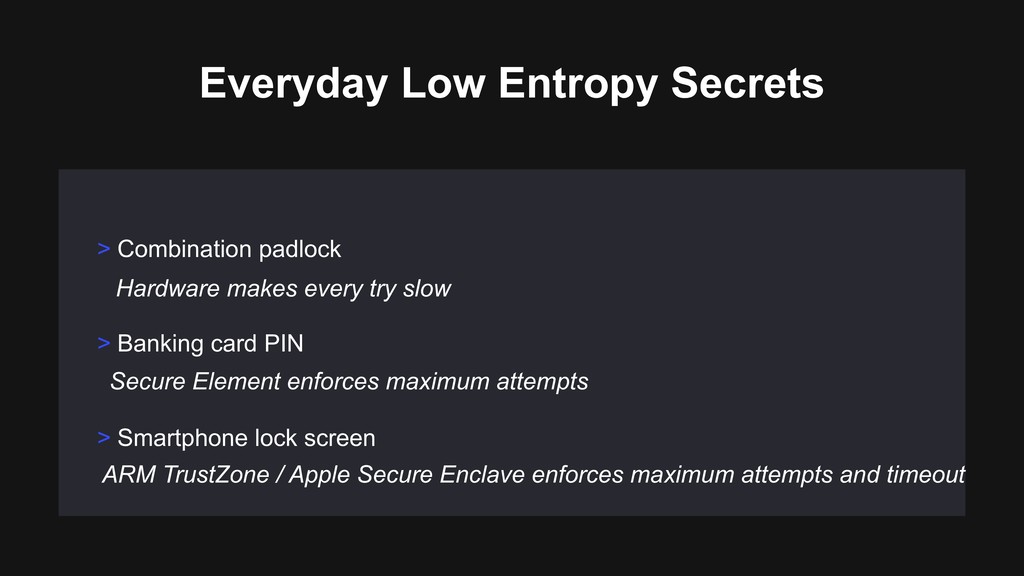
> Banking card PIN > Smartphone lock screen > Combination
padlock Everyday Low Entropy Secrets Hardware makes every try slow ARM TrustZone / Apple Secure Enclave enforces maximum attempts and timeout Secure Element enforces maximum attempts -
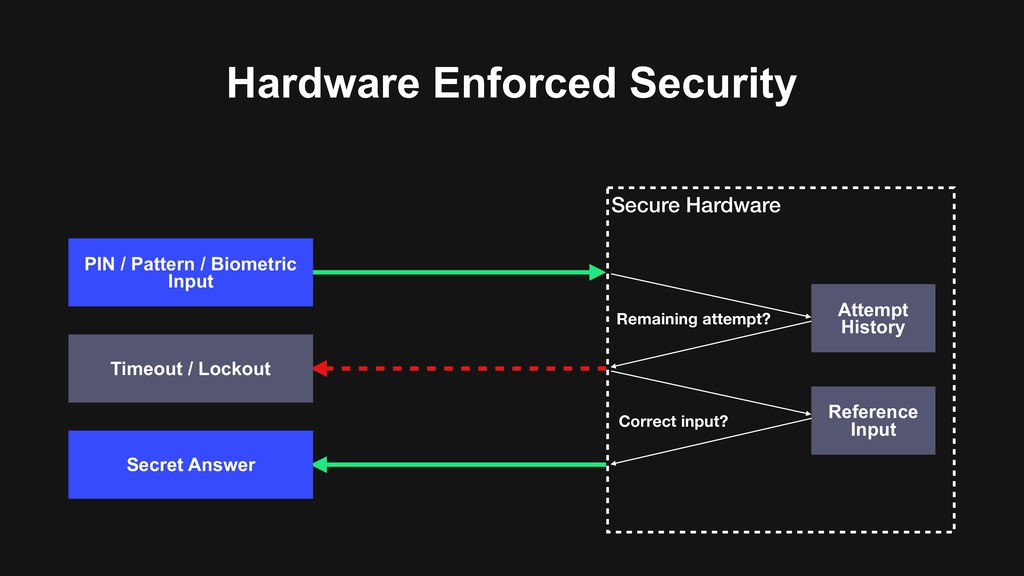
Hardware Enforced Security Secure Hardware Reference Input PIN / Pattern
/ Biometric Input Remaining attempt? Correct input? Attempt History Secret Answer Timeout / Lockout -
In Silicon We Trust > Countermeasure against physical attacks Disassembly,
side channels, fault injection, … > Separate management Signed updates, separate management key, memory erased on reset … > Isolated from the main system => Smaller attack surface to audit and secure Secure Hardware Advantages -
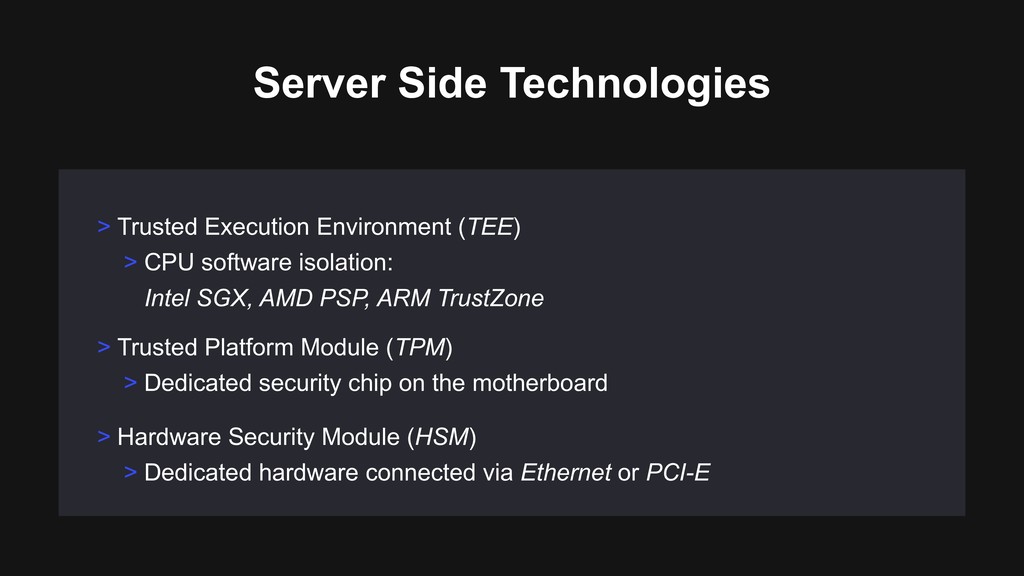
> Trusted Platform Module (TPM) > Dedicated security chip on
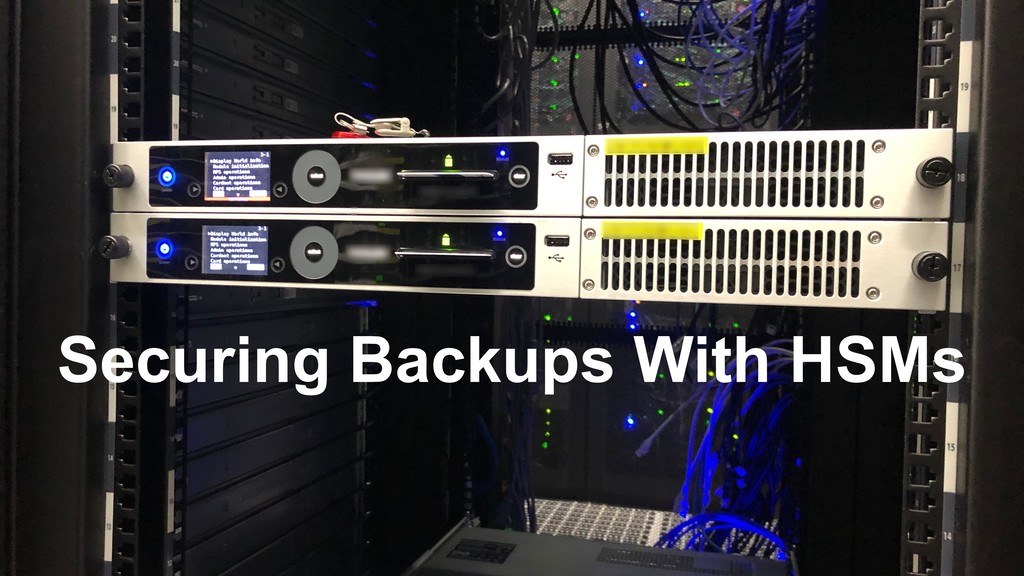
the motherboard > Hardware Security Module (HSM) > Dedicated hardware connected via Ethernet or PCI-E > Trusted Execution Environment (TEE) > CPU software isolation: Intel SGX, AMD PSP, ARM TrustZone Server Side Technologies -
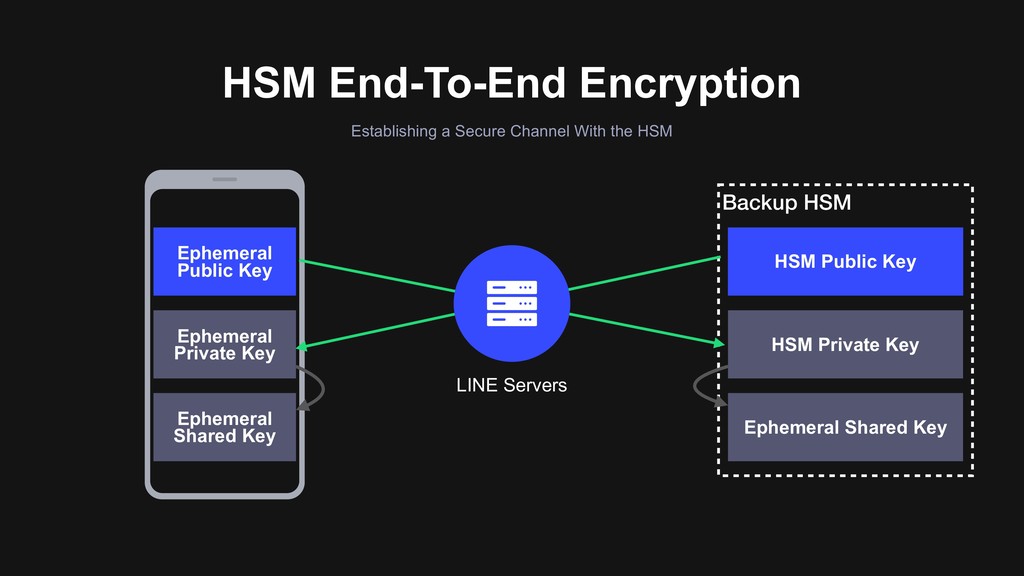
Backup HSM HSM End-To-End Encryption Ephemeral Private Key Ephemeral Public
Key Ephemeral Shared Key LINE Servers HSM Public Key HSM Private Key Ephemeral Shared Key Establishing a Secure Channel With the HSM -
Backup HSM User Device HSM Double Encryption LINE Servers Uploading
a Backup E E Letter Sealing Private Keys D PIN Input Ephemeral Shared Key Ephemeral Shared Key -
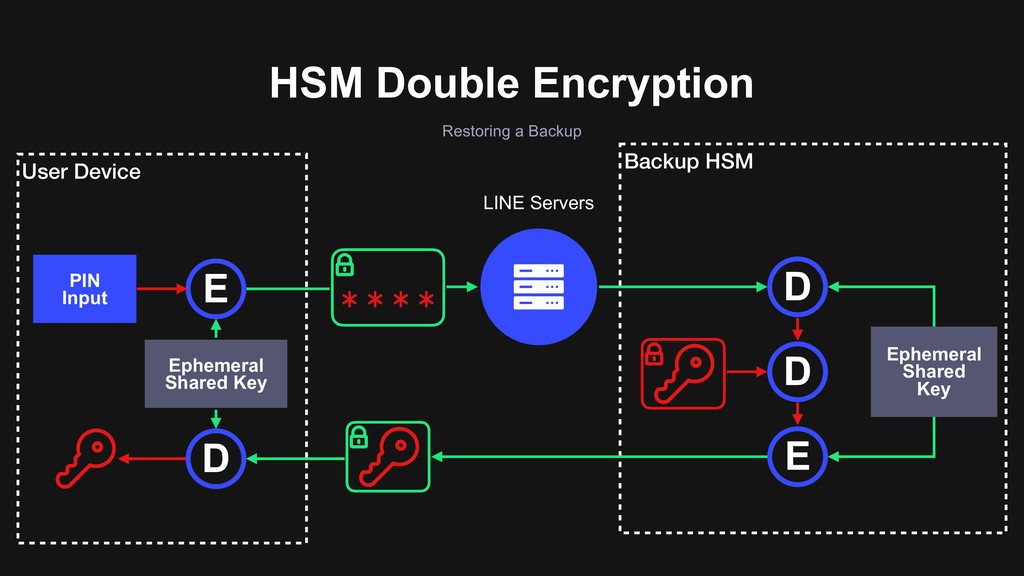
Backup HSM User Device HSM Double Encryption LINE Servers Restoring
a Backup E D PIN Input Ephemeral Shared Key Ephemeral Shared Key **** D E D -
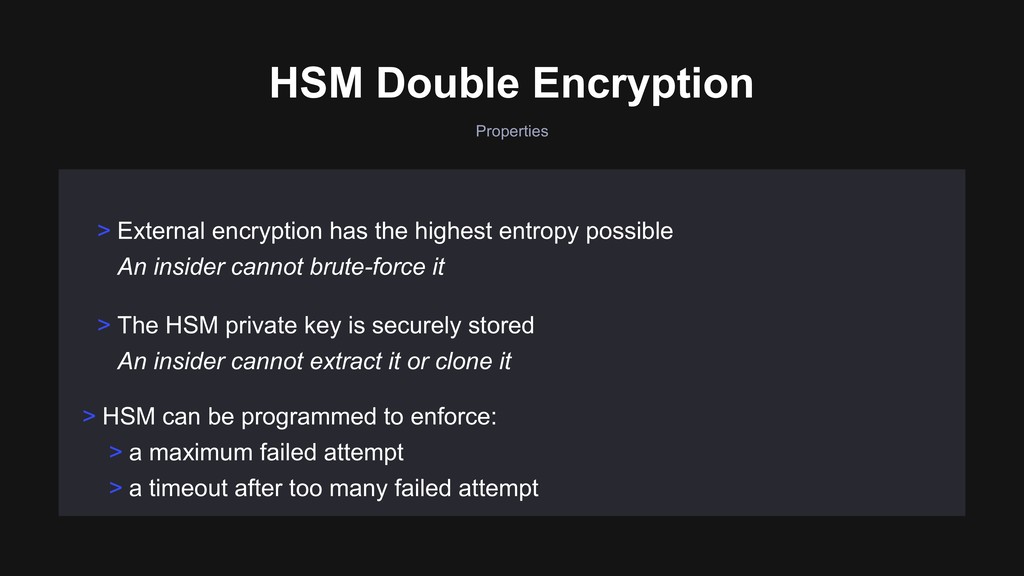
> HSM can be programmed to enforce: > a maximum
failed attempt > a timeout after too many failed attempt > The HSM private key is securely stored An insider cannot extract it or clone it > External encryption has the highest entropy possible An insider cannot brute-force it HSM Double Encryption Properties -
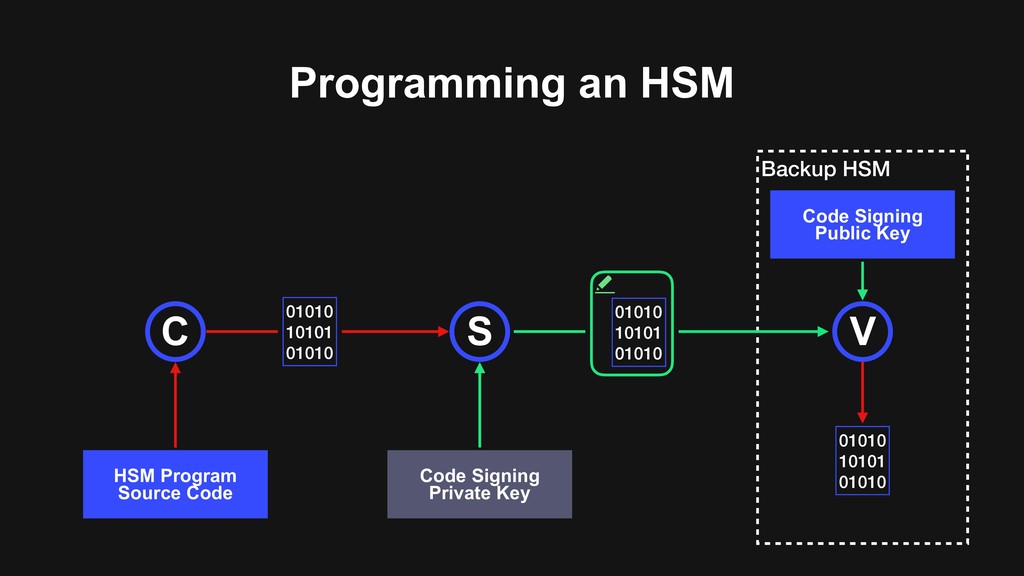
Programming an HSM S Backup HSM V Code Signing Private
Key Code Signing Public Key HSM Program Source Code C 01010 10101 01010 01010 10101 01010 01010 10101 01010 -
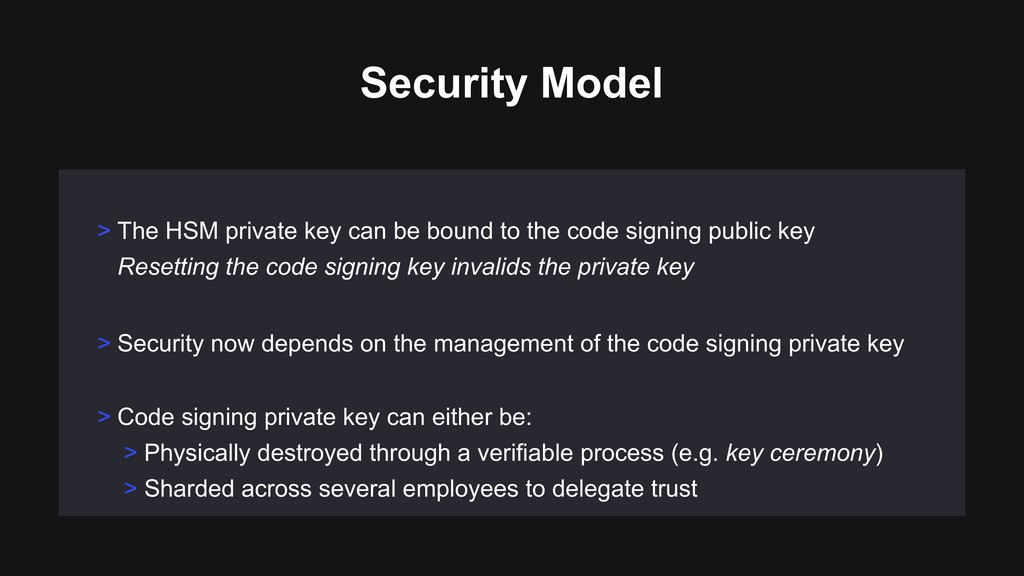
> Security now depends on the management of the code
signing private key > Code signing private key can either be: > Physically destroyed through a verifiable process (e.g. key ceremony) > Sharded across several employees to delegate trust > The HSM private key can be bound to the code signing public key Resetting the code signing key invalids the private key Security Model -
> Cryptography and secure hardware can enable new compromise >
Already used by other tech giants, LINE is experimenting with it > Balancing UX and Security is hard Last Words