Share
Embed
2022-03-24_Doyensec - Infrastructure Review
A private talk delivered for the Doyensec's team on 2022-03-24.
The talk is an extract of the blog post: What to look for when reviewing a company's infrastructure
Marco Lancini
March 24, 2022
Transcript
38 slides
-
2 securitybite.com 👋 Hello! I am Marco Lancini You can
find me at @lancinimarco https://www.marcolancini.it ▪ Work Life ◦ Started as a pentester at CEFRIEL, MWR ◦ Built security functions at Mastercard, Thought Machine, GitLab ◦ Currently, I'm a Staff Cloud Security Engineer at GitLab ▪ Outside of Work ◦ Curator of CloudSecList and CloudSecDocs ◦ Member of CNCF Security Technical Advisory Group (STAG) ◦ Maintainer of Cartography ◦ AWS Community Builder -
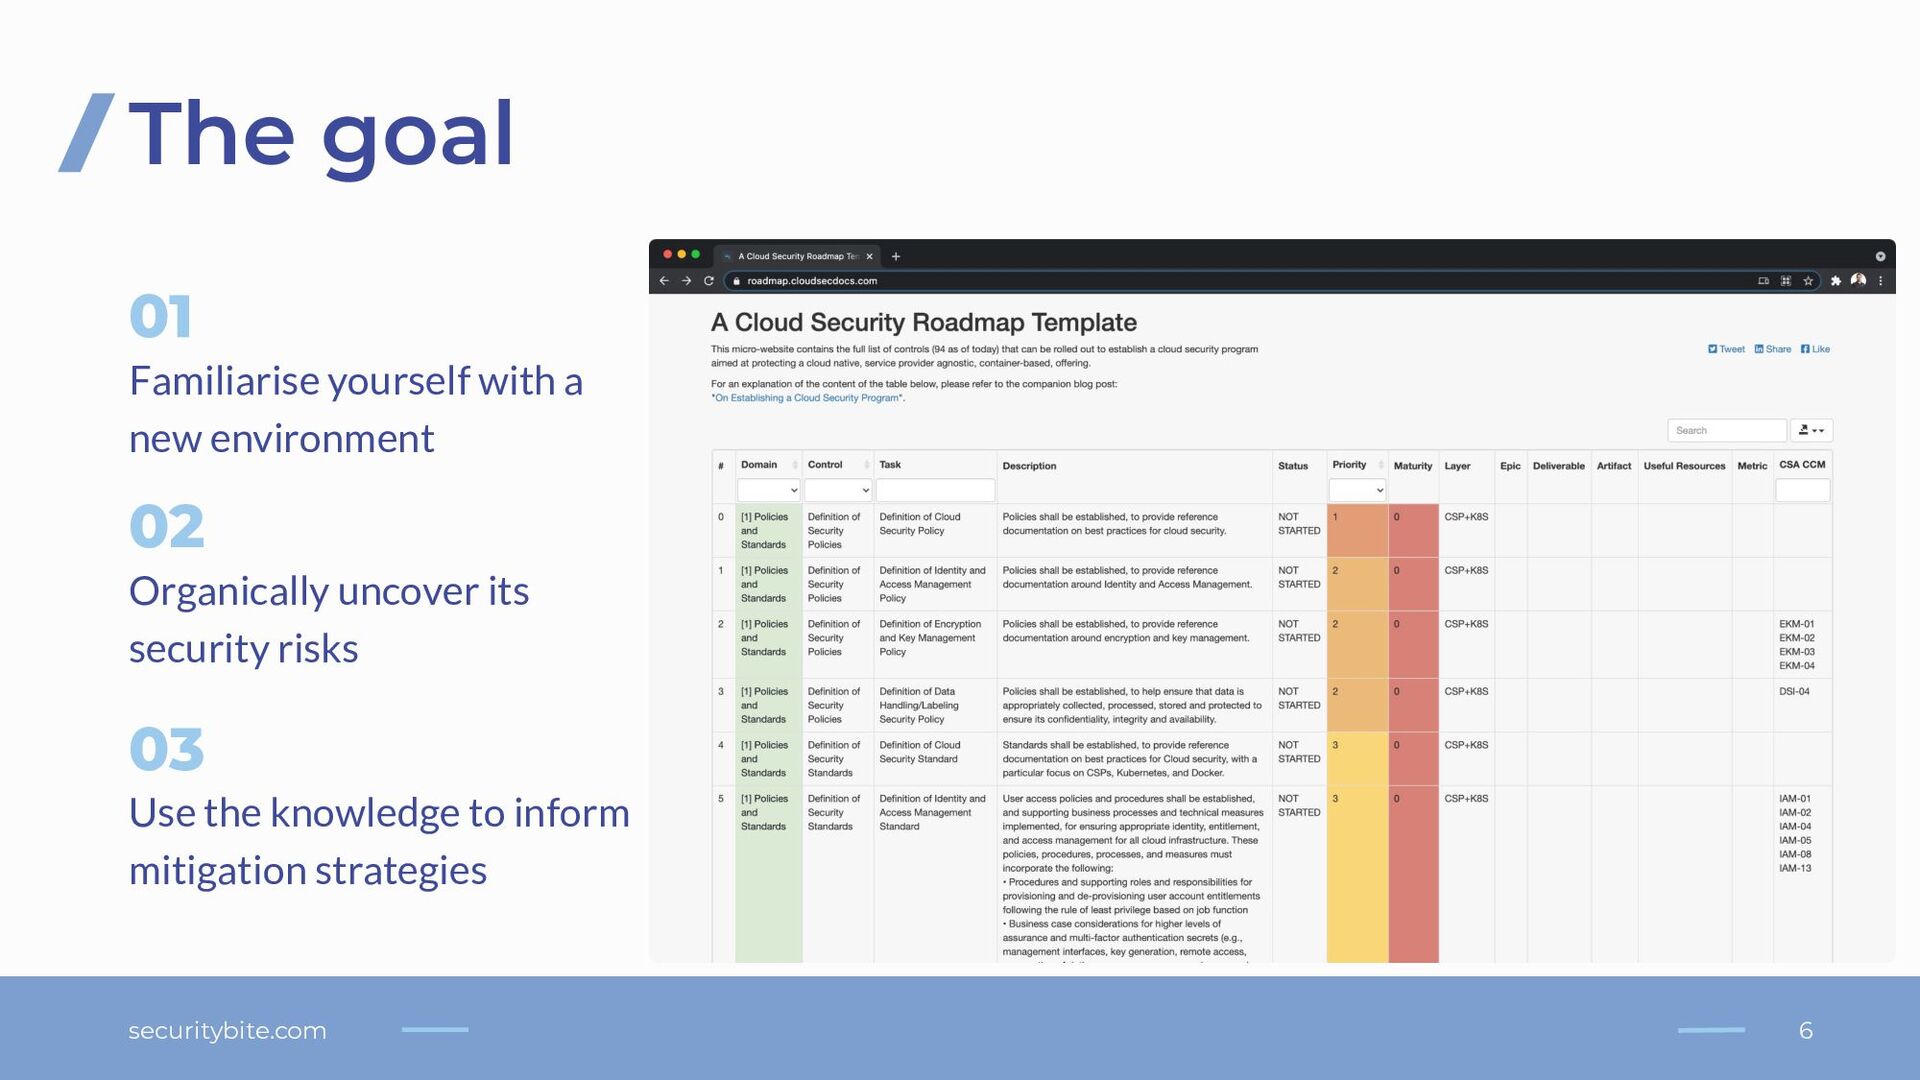
6 securitybite.com Familiarise yourself with a new environment 01 Organically
uncover its security risks 02 Use the knowledge to inform mitigation strategies 03 The goal -
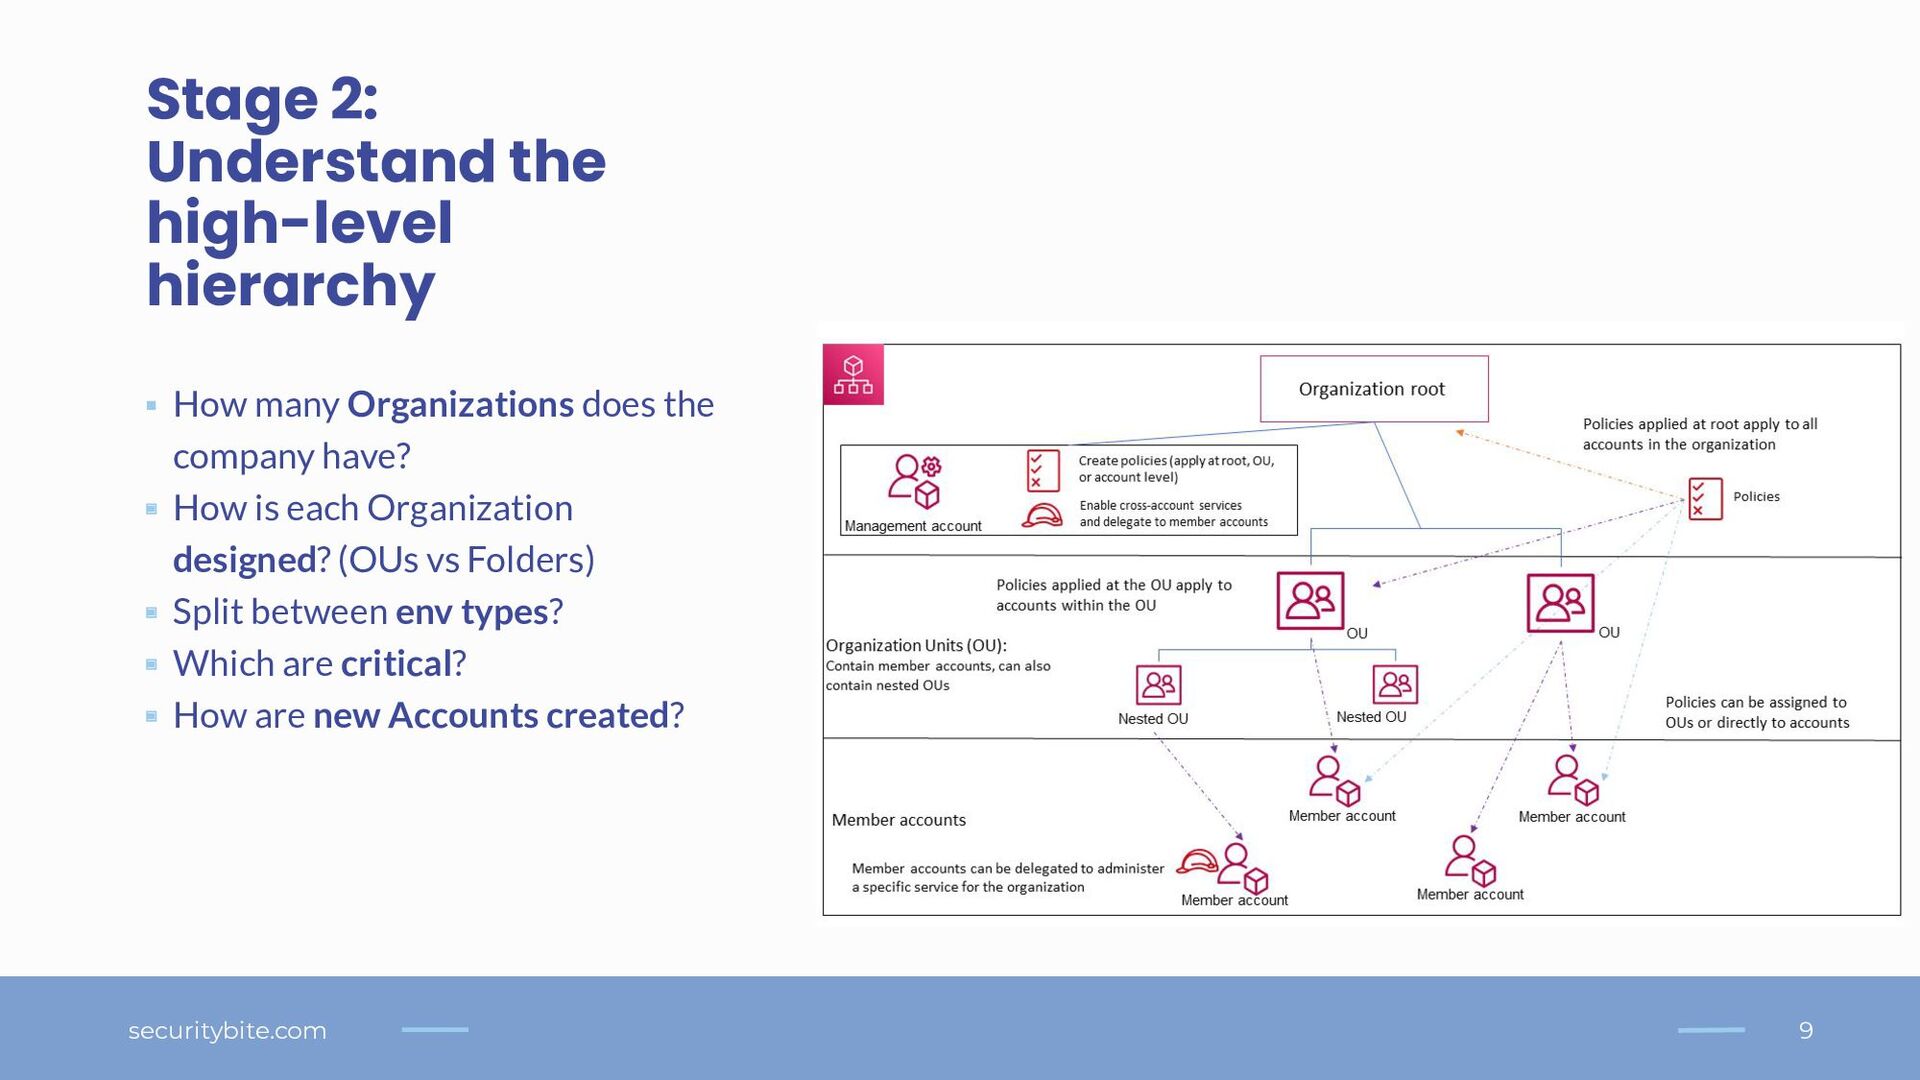
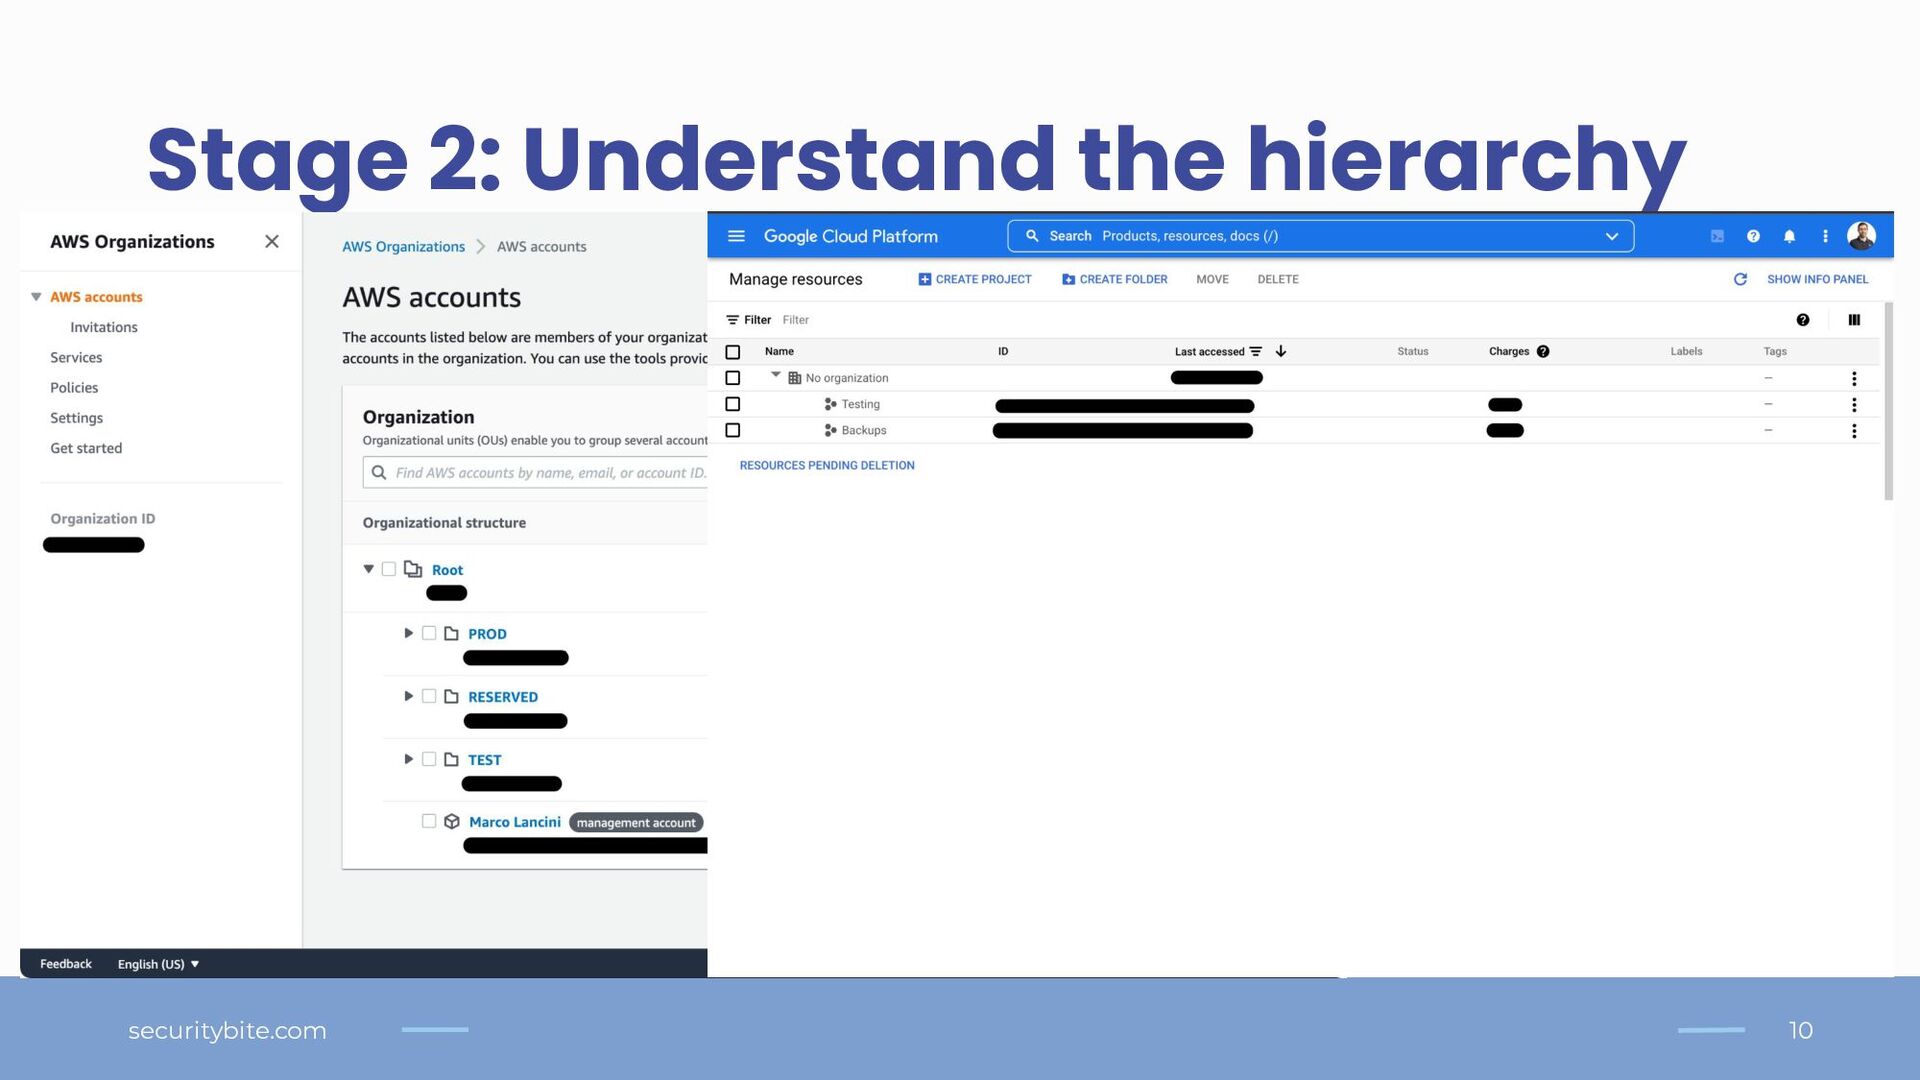
9 securitybite.com Stage 2: Understand the high-level hierarchy ▪ How
many Organizations does the company have? ▪ How is each Organization designed? (OUs vs Folders) ▪ Split between env types? ▪ Which are critical? ▪ How are new Accounts created? -
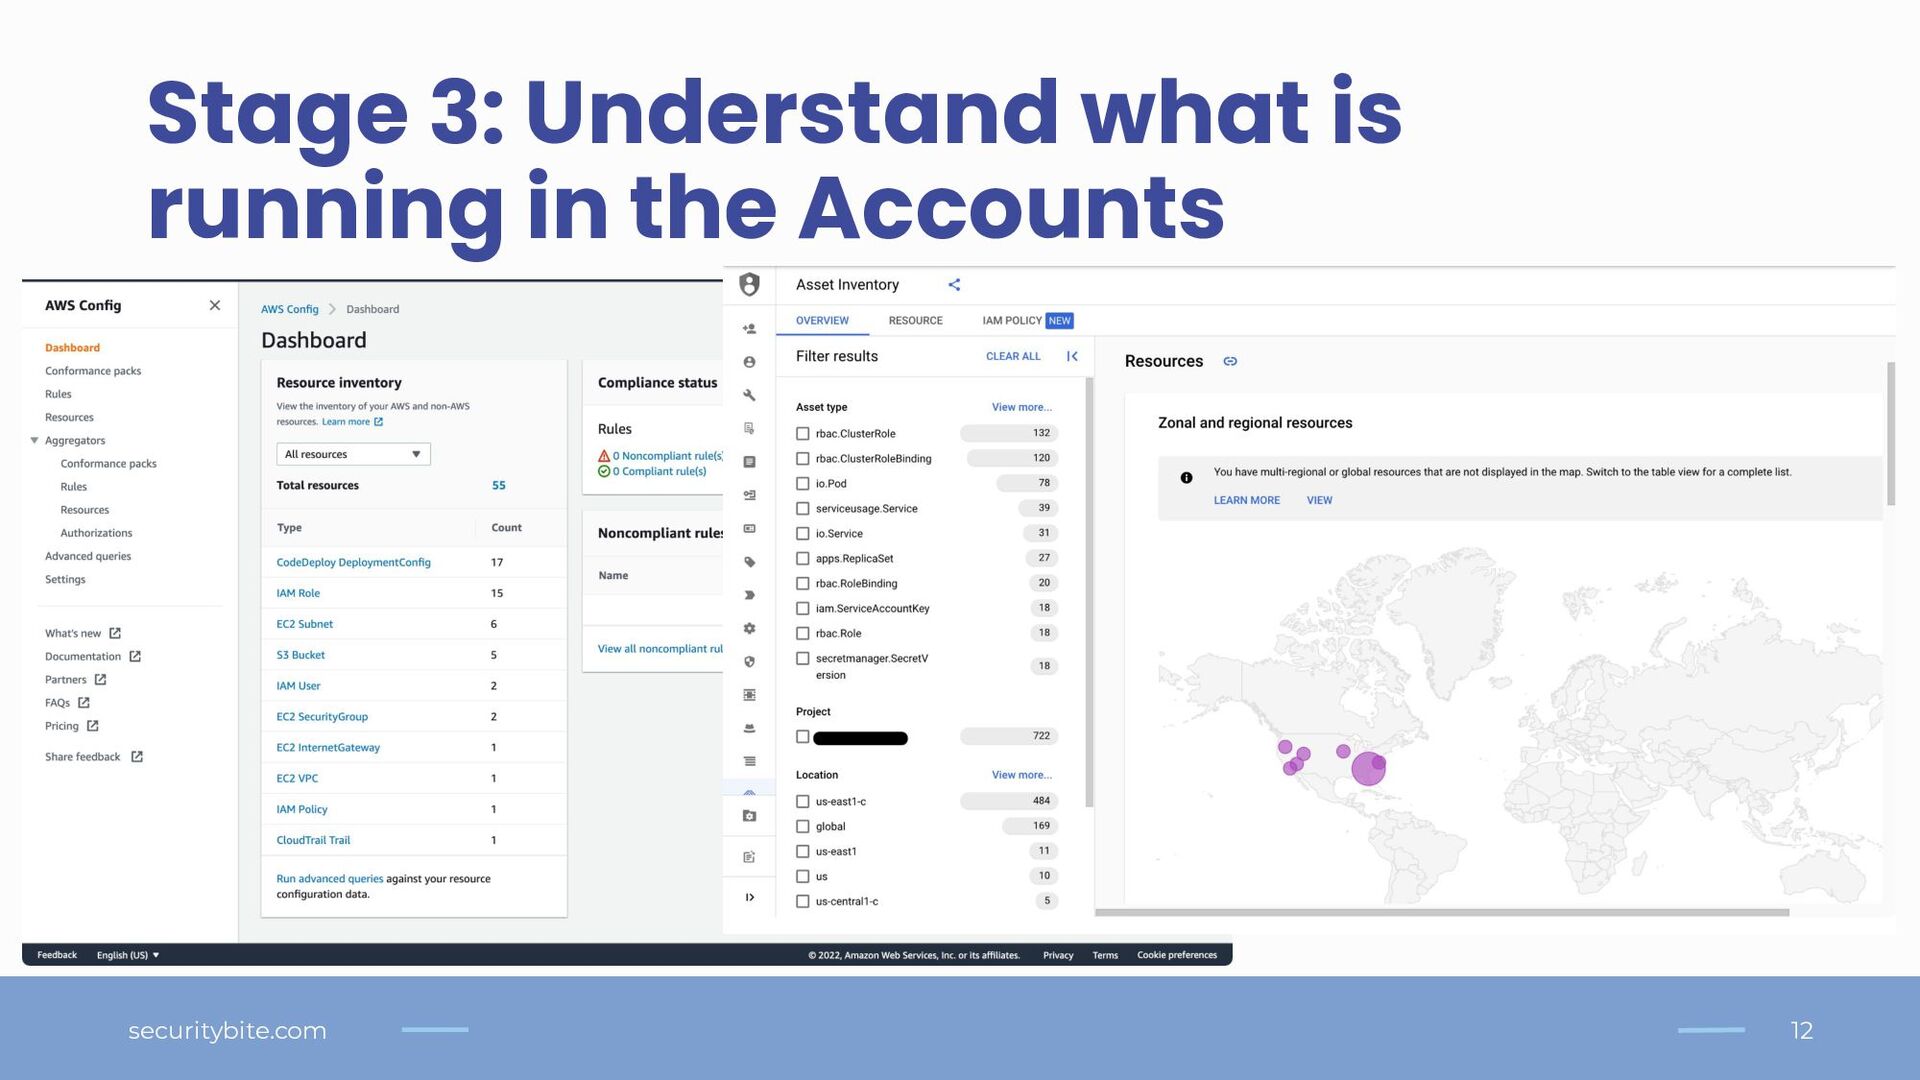
11 securitybite.com Stage 3: Understand what is running in the
Accounts ▪ Container-heavy? (K8s, ECS,...) ▪ Serverless? (Lambda, Cloud Function) ▪ VM-based? (EC2, …) -
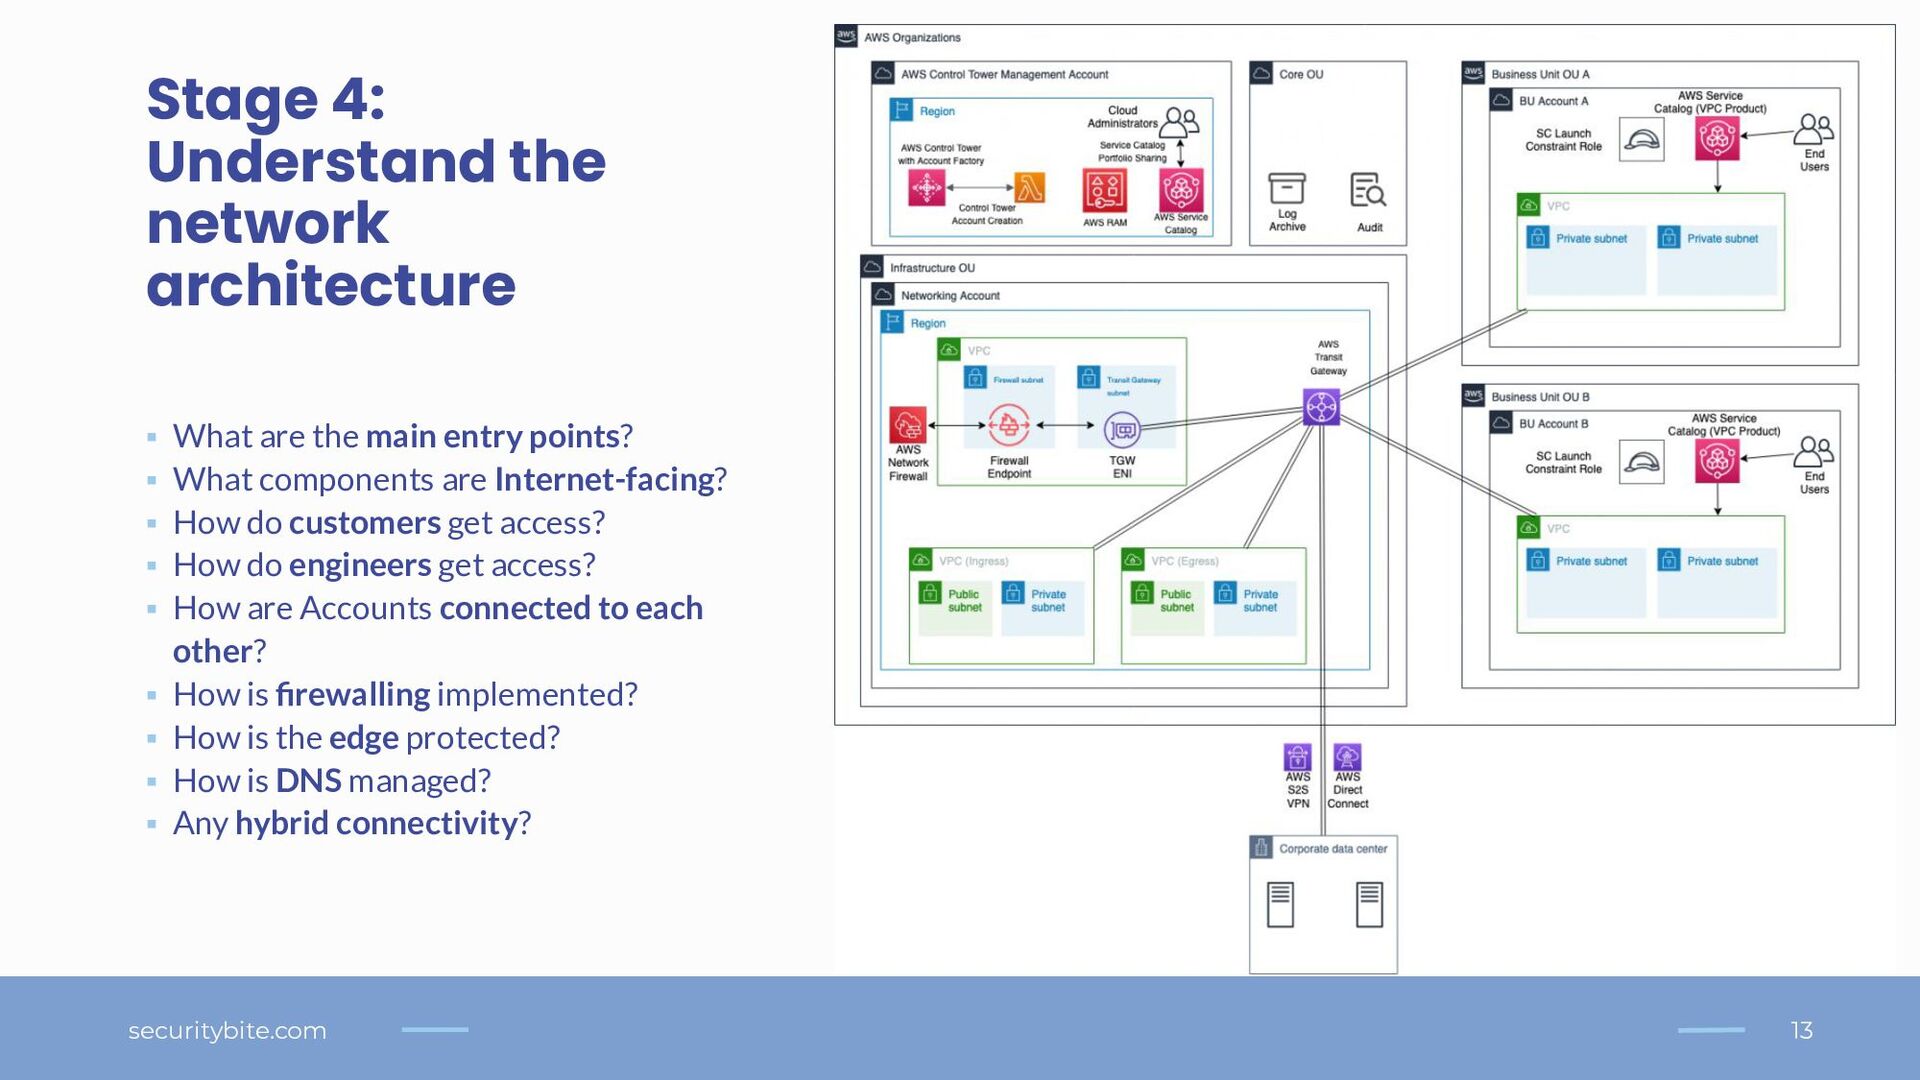
13 securitybite.com Stage 4: Understand the network architecture ▪ What
are the main entry points? ▪ What components are Internet-facing? ▪ How do customers get access? ▪ How do engineers get access? ▪ How are Accounts connected to each other? ▪ How is firewalling implemented? ▪ How is the edge protected? ▪ How is DNS managed? ▪ Any hybrid connectivity? -
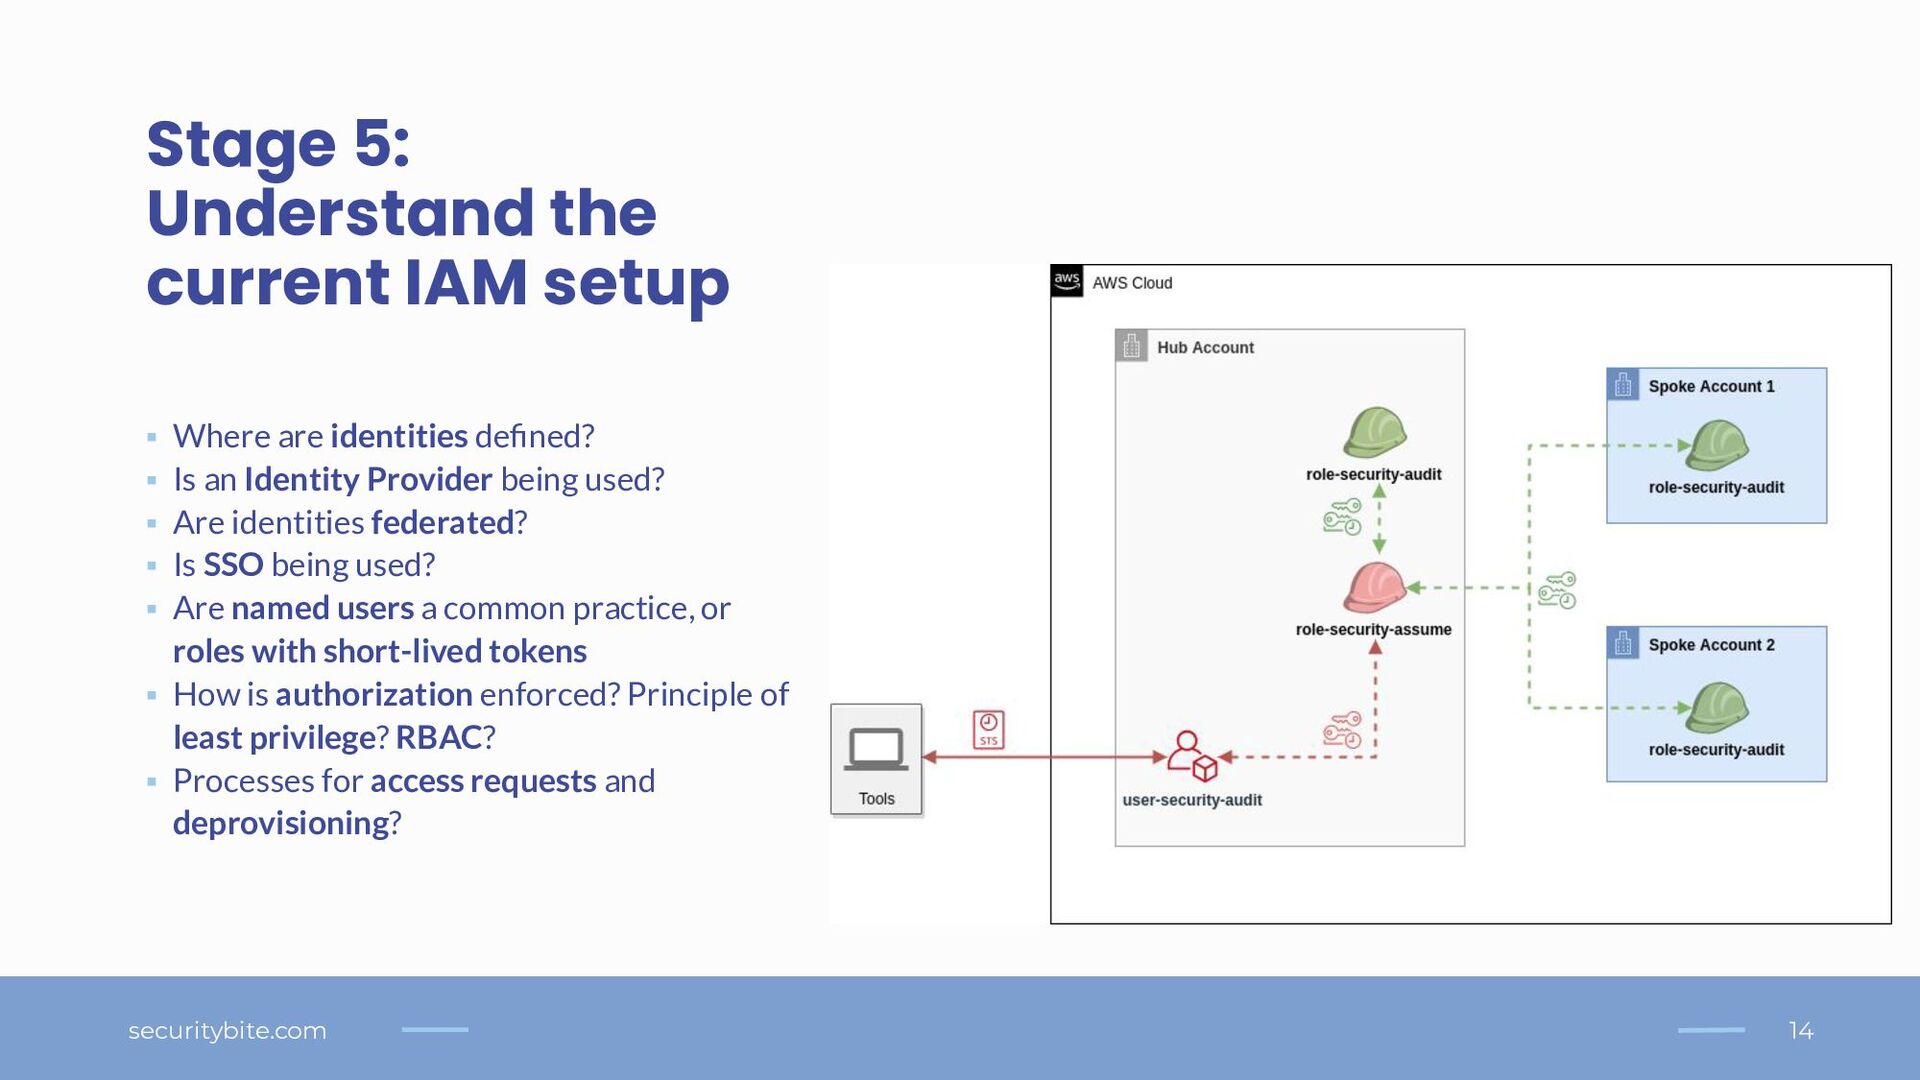
14 securitybite.com Stage 5: Understand the current IAM setup ▪
Where are identities defined? ▪ Is an Identity Provider being used? ▪ Are identities federated? ▪ Is SSO being used? ▪ Are named users a common practice, or roles with short-lived tokens ▪ How is authorization enforced? Principle of least privilege? RBAC? ▪ Processes for access requests and deprovisioning? -
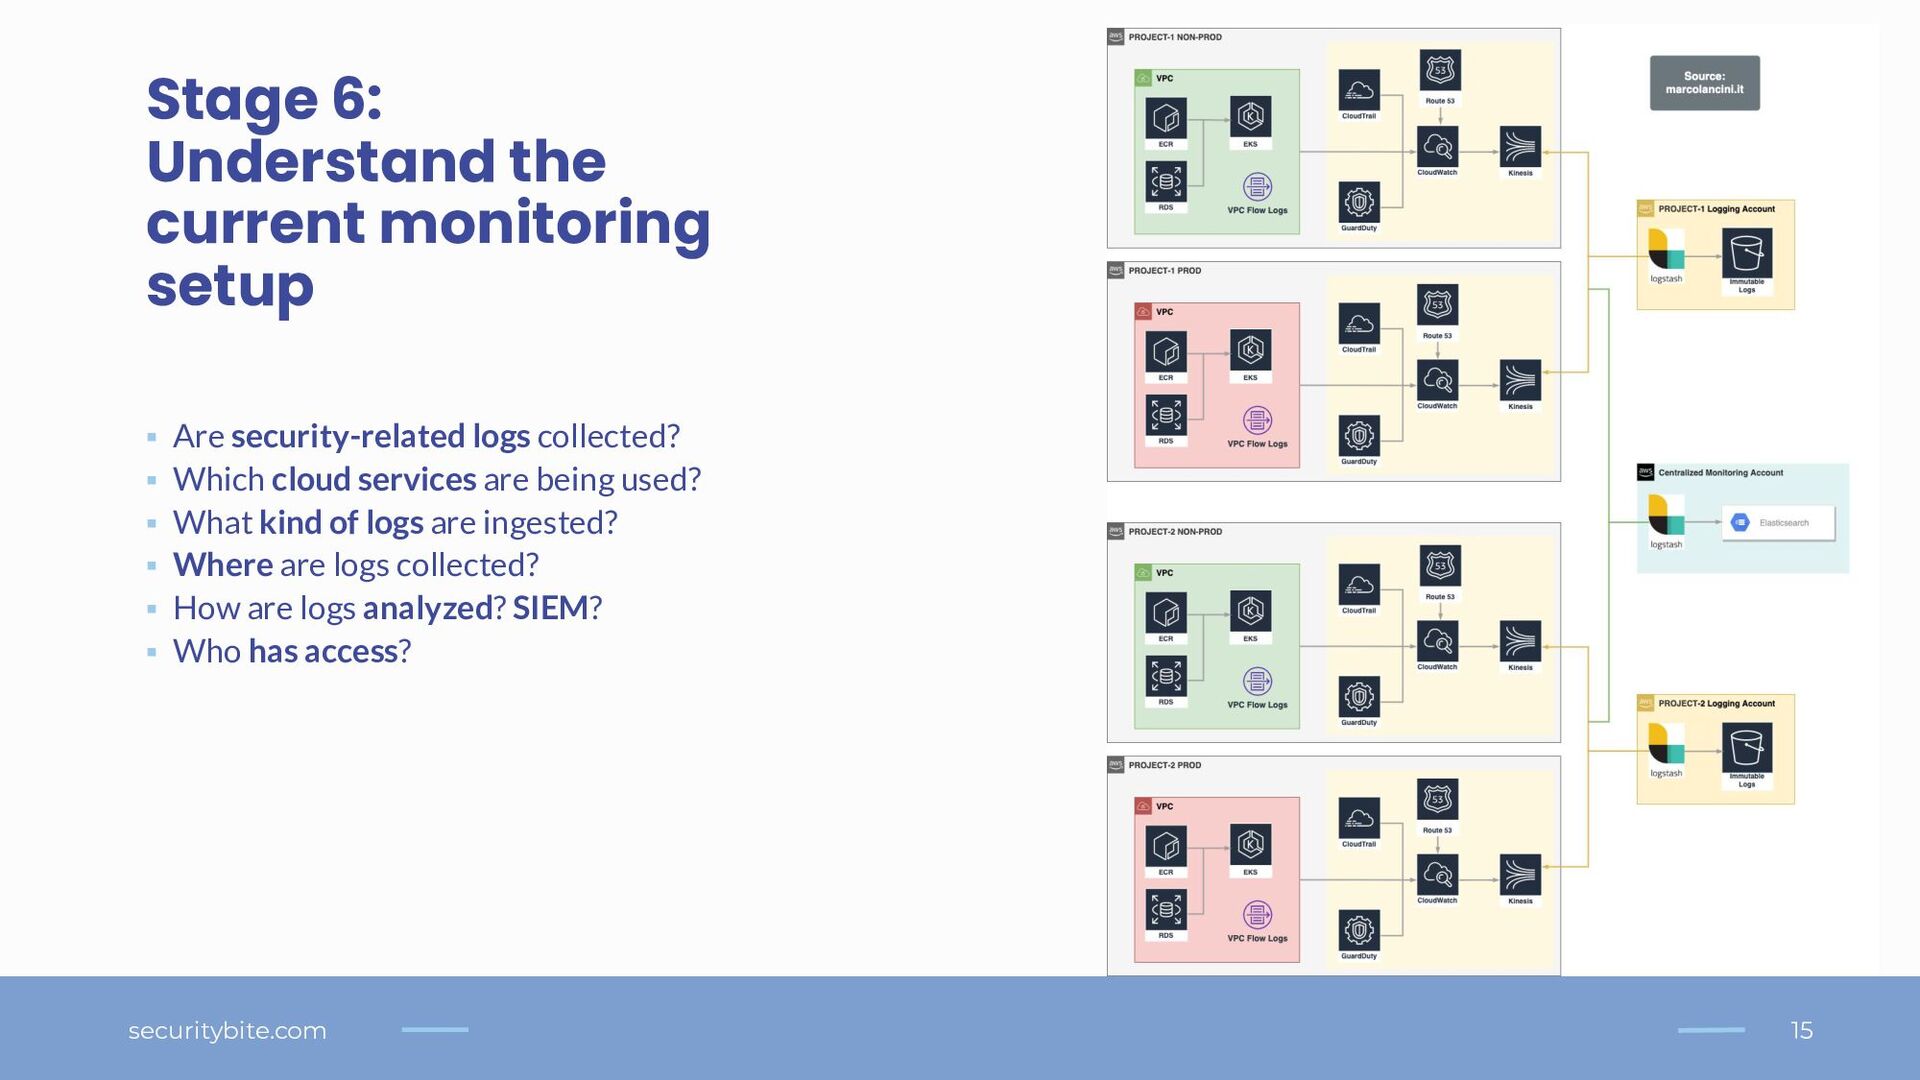
15 securitybite.com Stage 6: Understand the current monitoring setup ▪
Are security-related logs collected? ▪ Which cloud services are being used? ▪ What kind of logs are ingested? ▪ Where are logs collected? ▪ How are logs analyzed? SIEM? ▪ Who has access? -
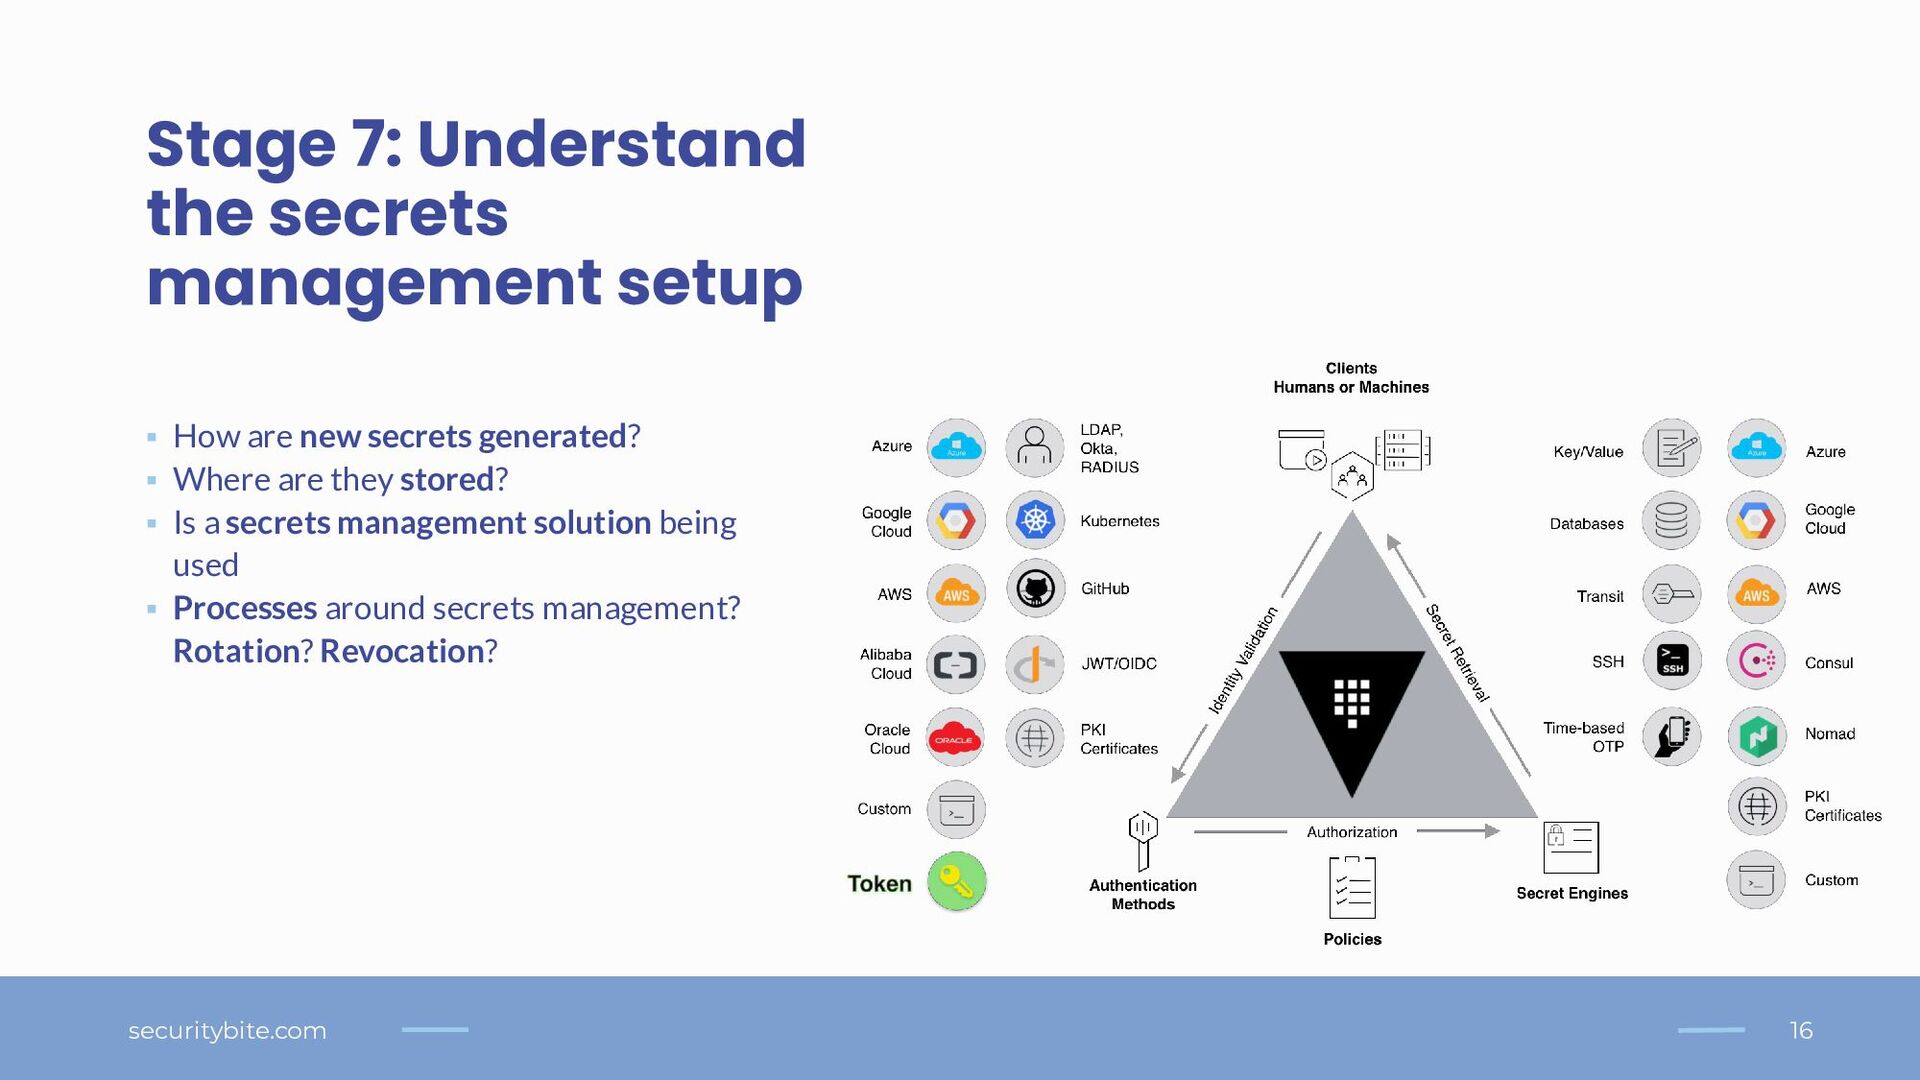
16 securitybite.com Stage 7: Understand the secrets management setup ▪
How are new secrets generated? ▪ Where are they stored? ▪ Is a secrets management solution being used ▪ Processes around secrets management? Rotation? Revocation? -
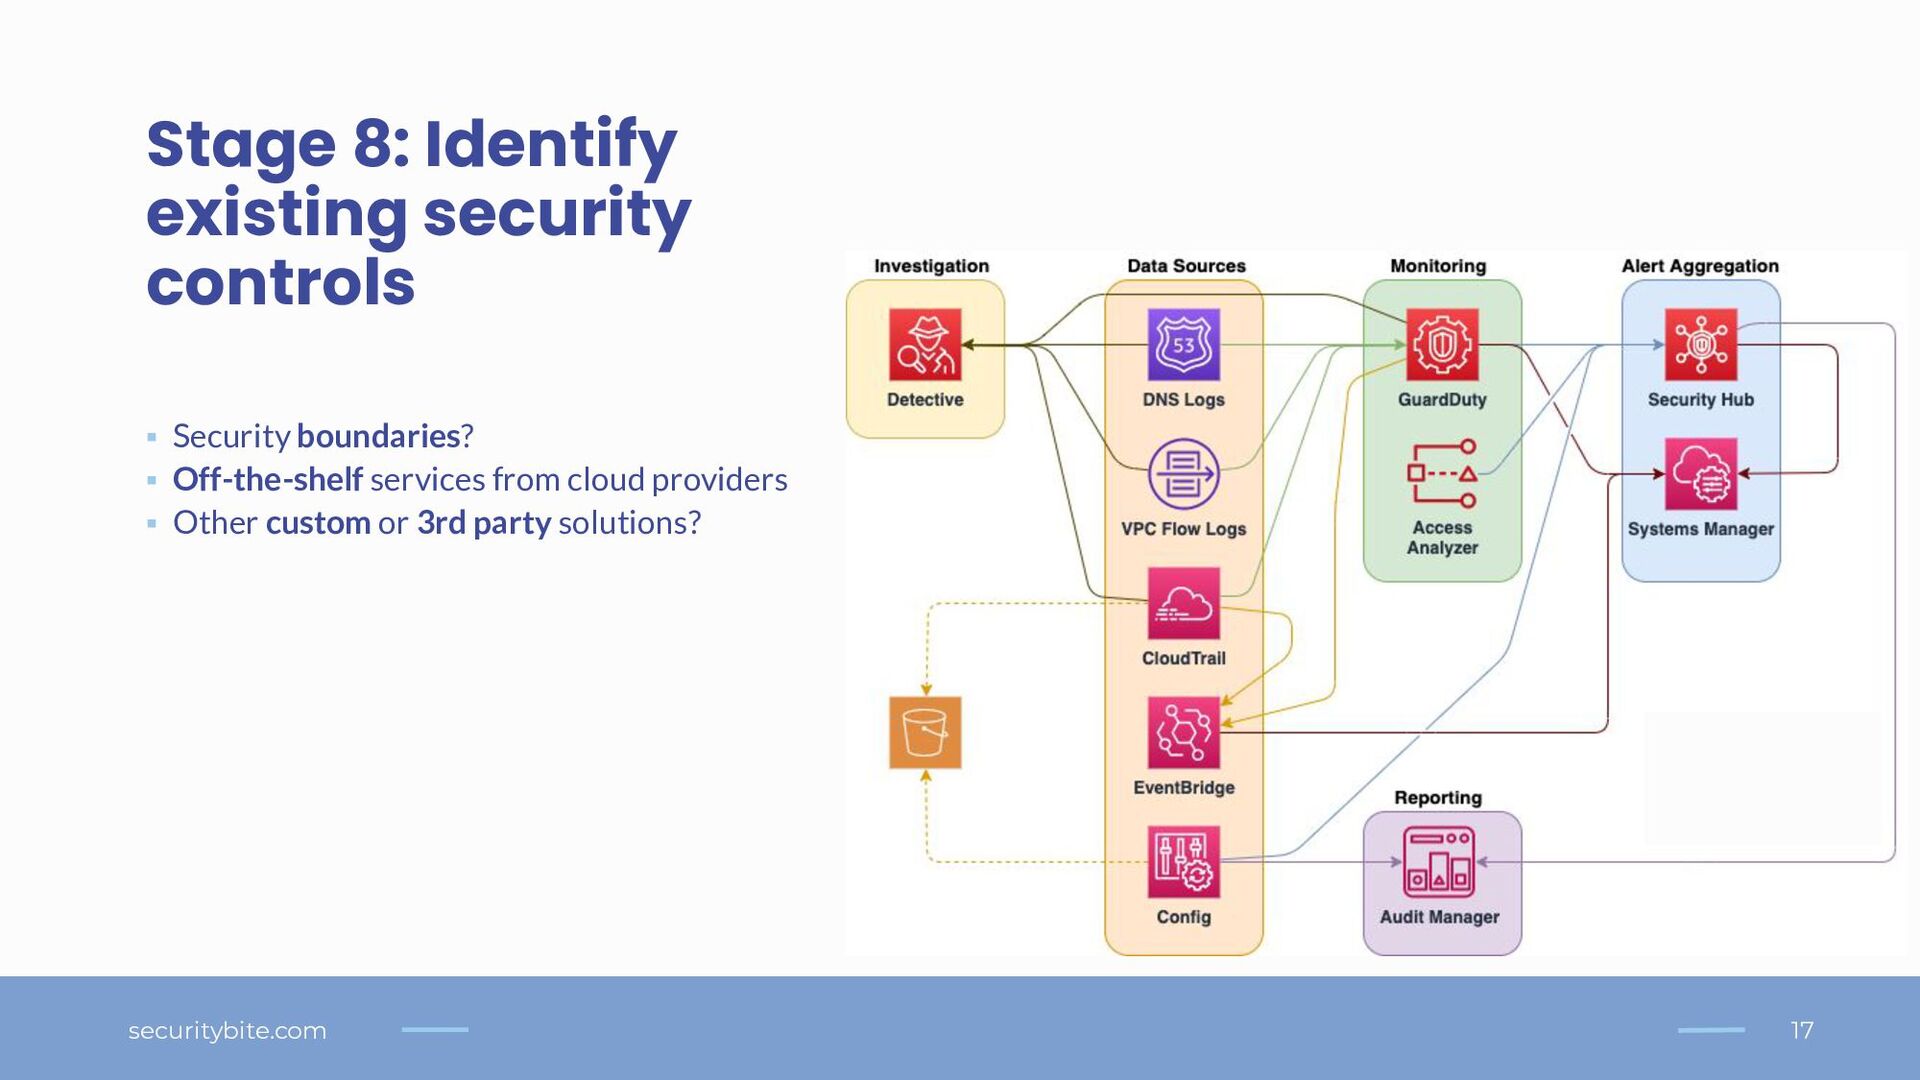
17 securitybite.com Stage 8: Identify existing security controls ▪ Security
boundaries? ▪ Off-the-shelf services from cloud providers ▪ Other custom or 3rd party solutions? -
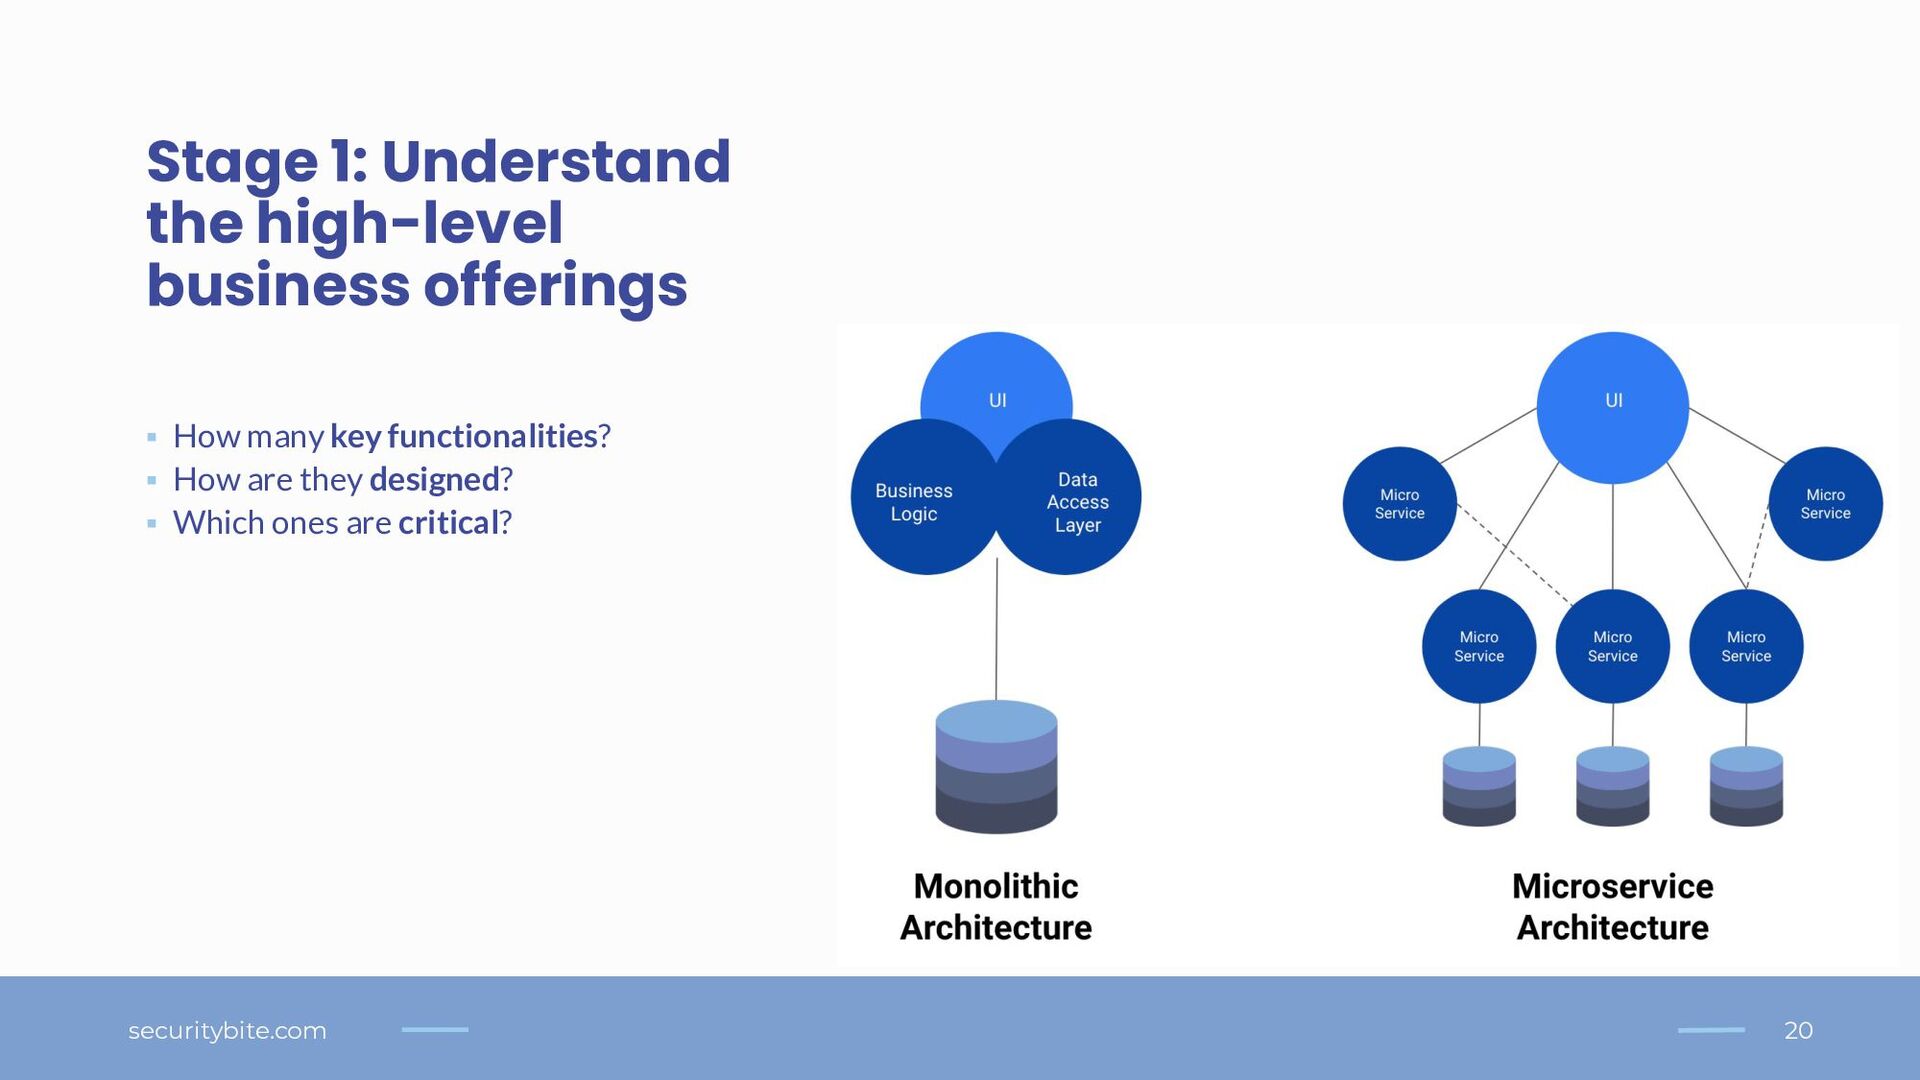
20 securitybite.com Stage 1: Understand the high-level business offerings ▪
How many key functionalities? ▪ How are they designed? ▪ Which ones are critical? -
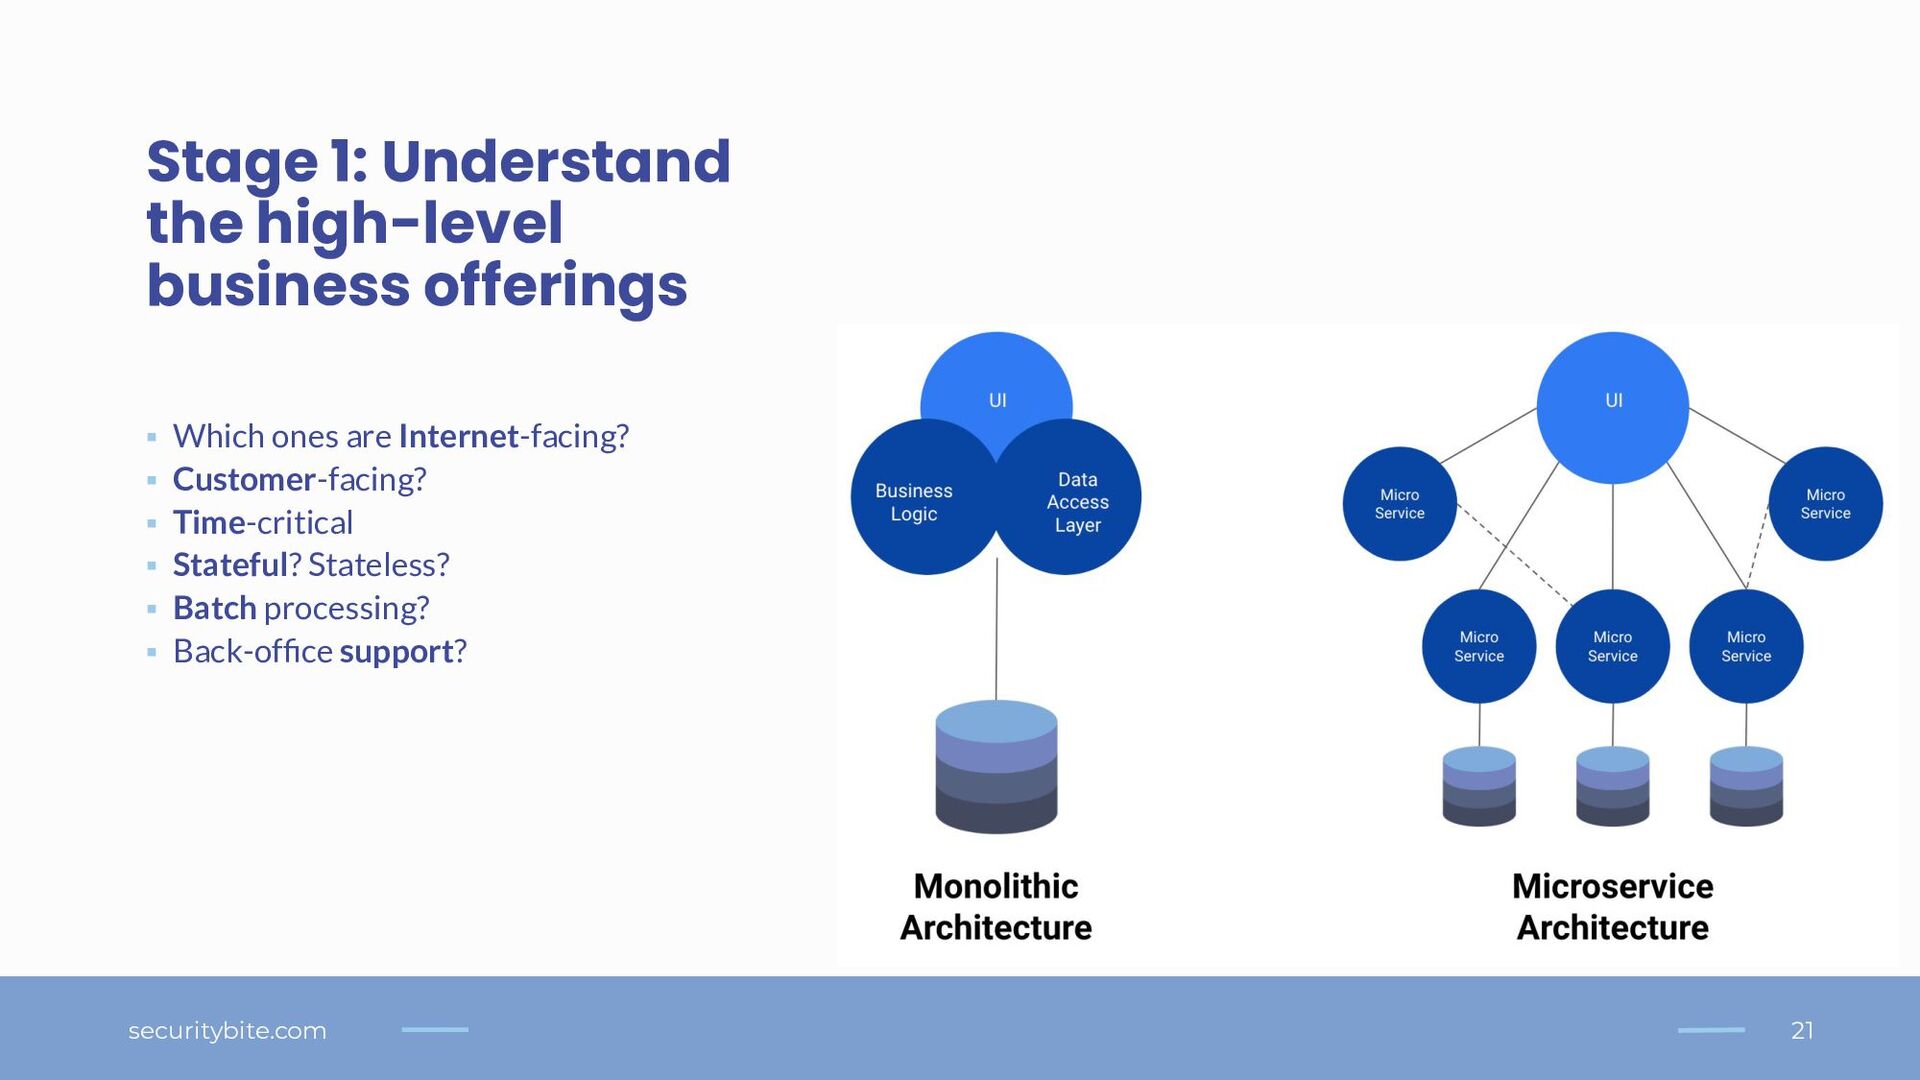
21 securitybite.com Stage 1: Understand the high-level business offerings ▪
Which ones are Internet-facing? ▪ Customer-facing? ▪ Time-critical ▪ Stateful? Stateless? ▪ Batch processing? ▪ Back-office support? -
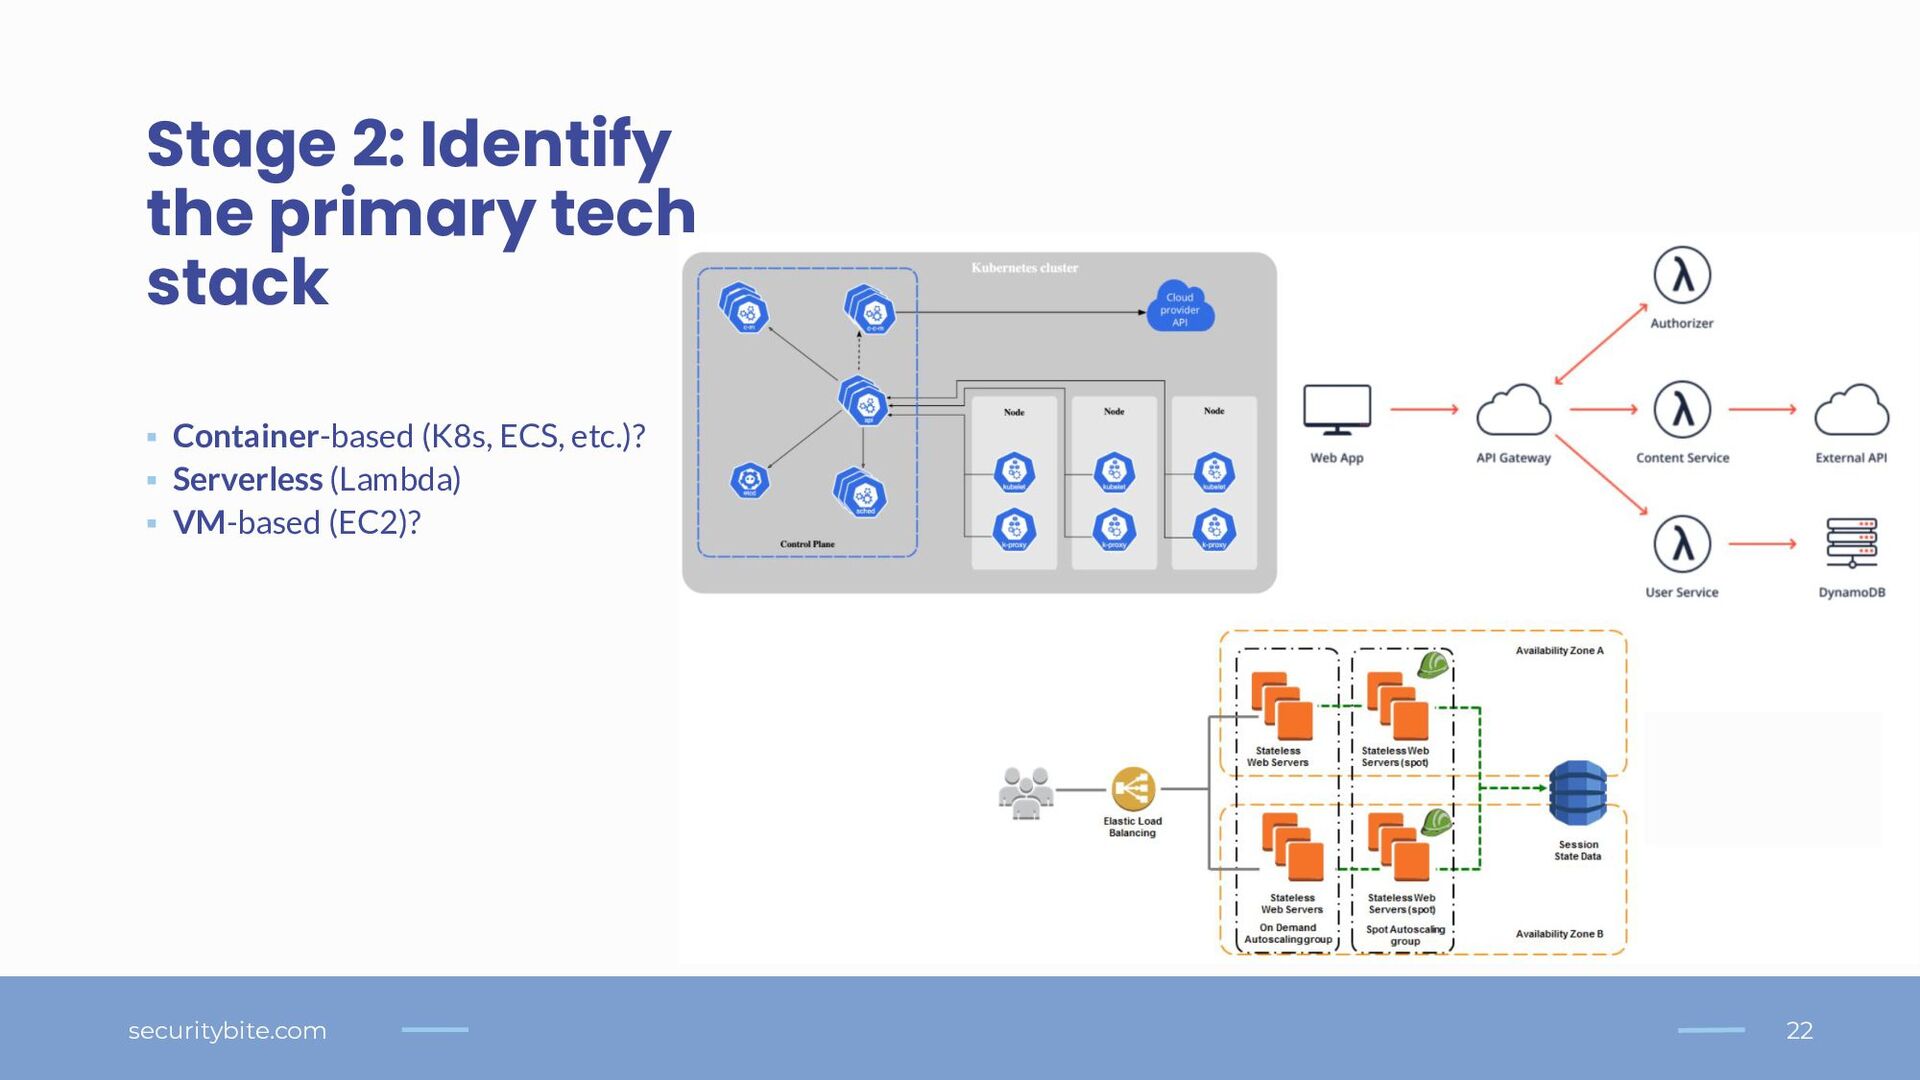
22 securitybite.com Stage 2: Identify the primary tech stack ▪
Container-based (K8s, ECS, etc.)? ▪ Serverless (Lambda) ▪ VM-based (EC2)? -
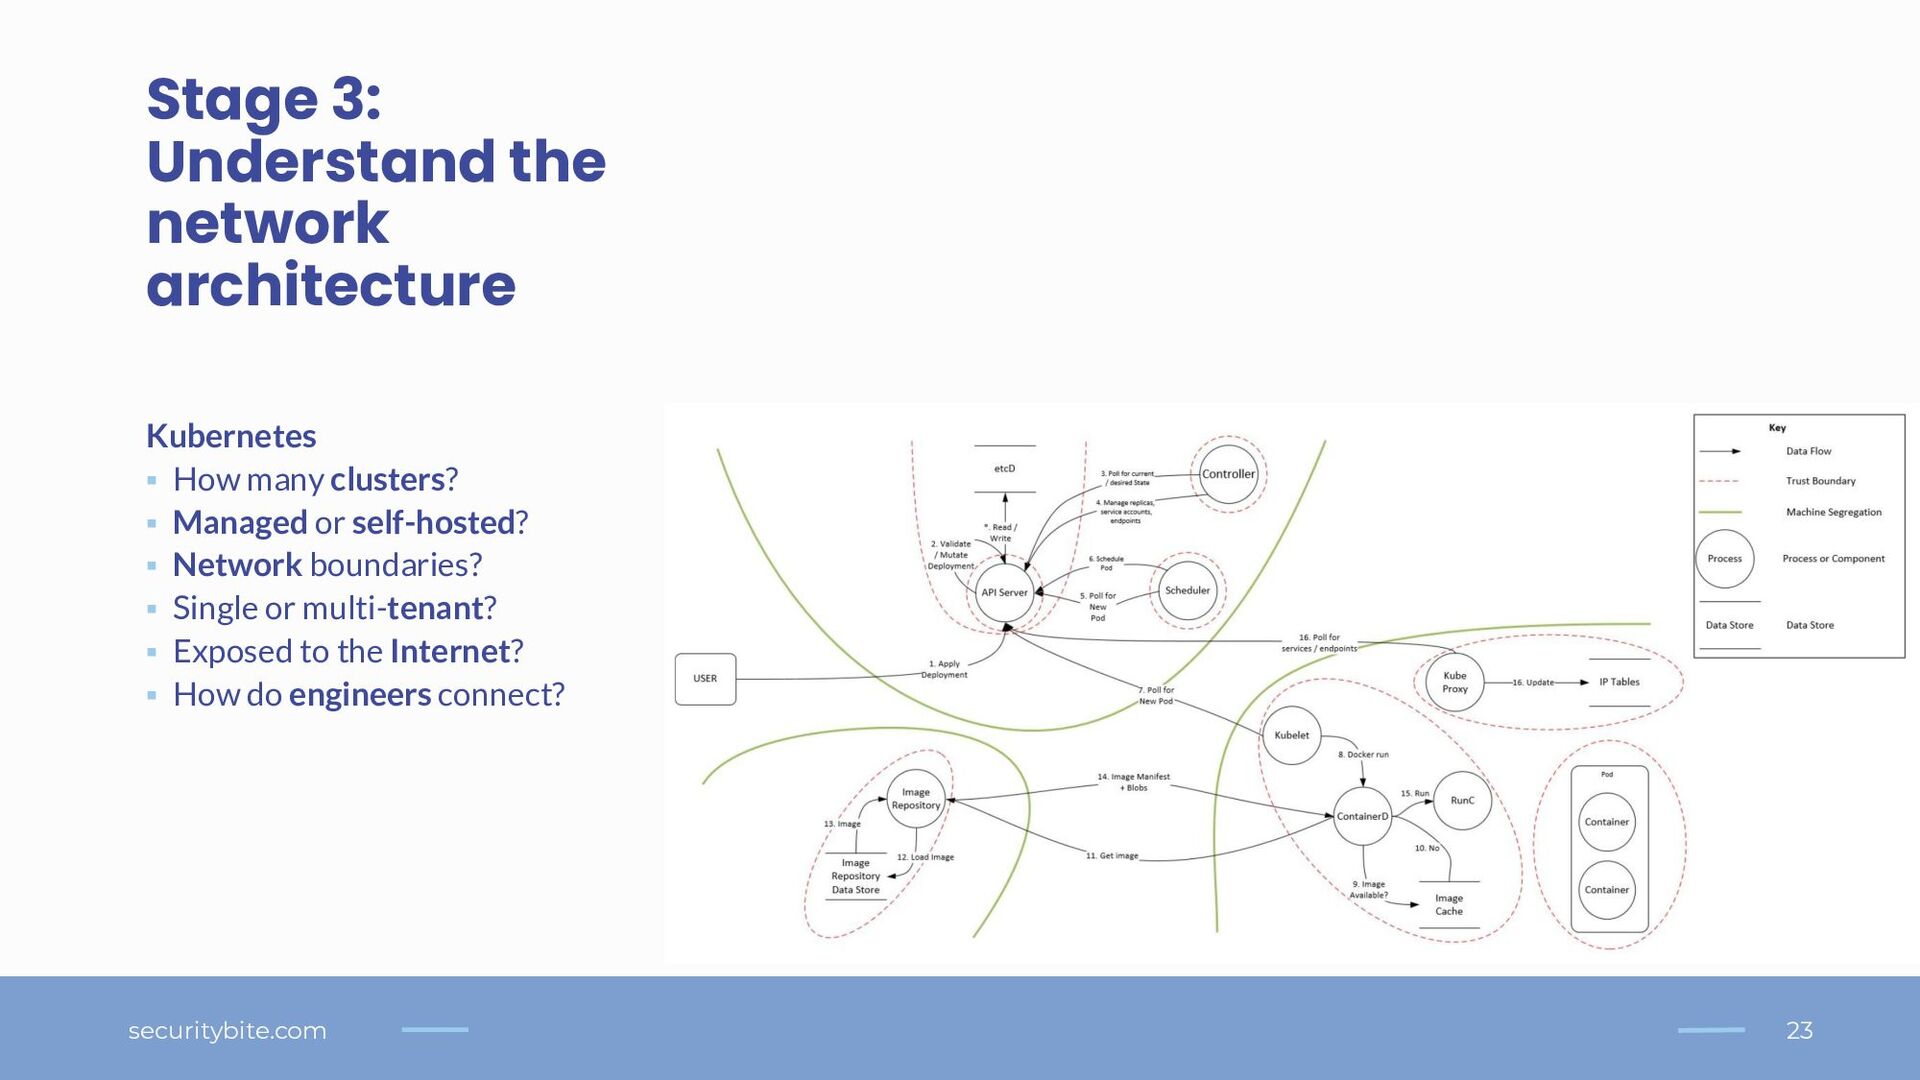
23 securitybite.com Stage 3: Understand the network architecture Kubernetes ▪
How many clusters? ▪ Managed or self-hosted? ▪ Network boundaries? ▪ Single or multi-tenant? ▪ Exposed to the Internet? ▪ How do engineers connect? -
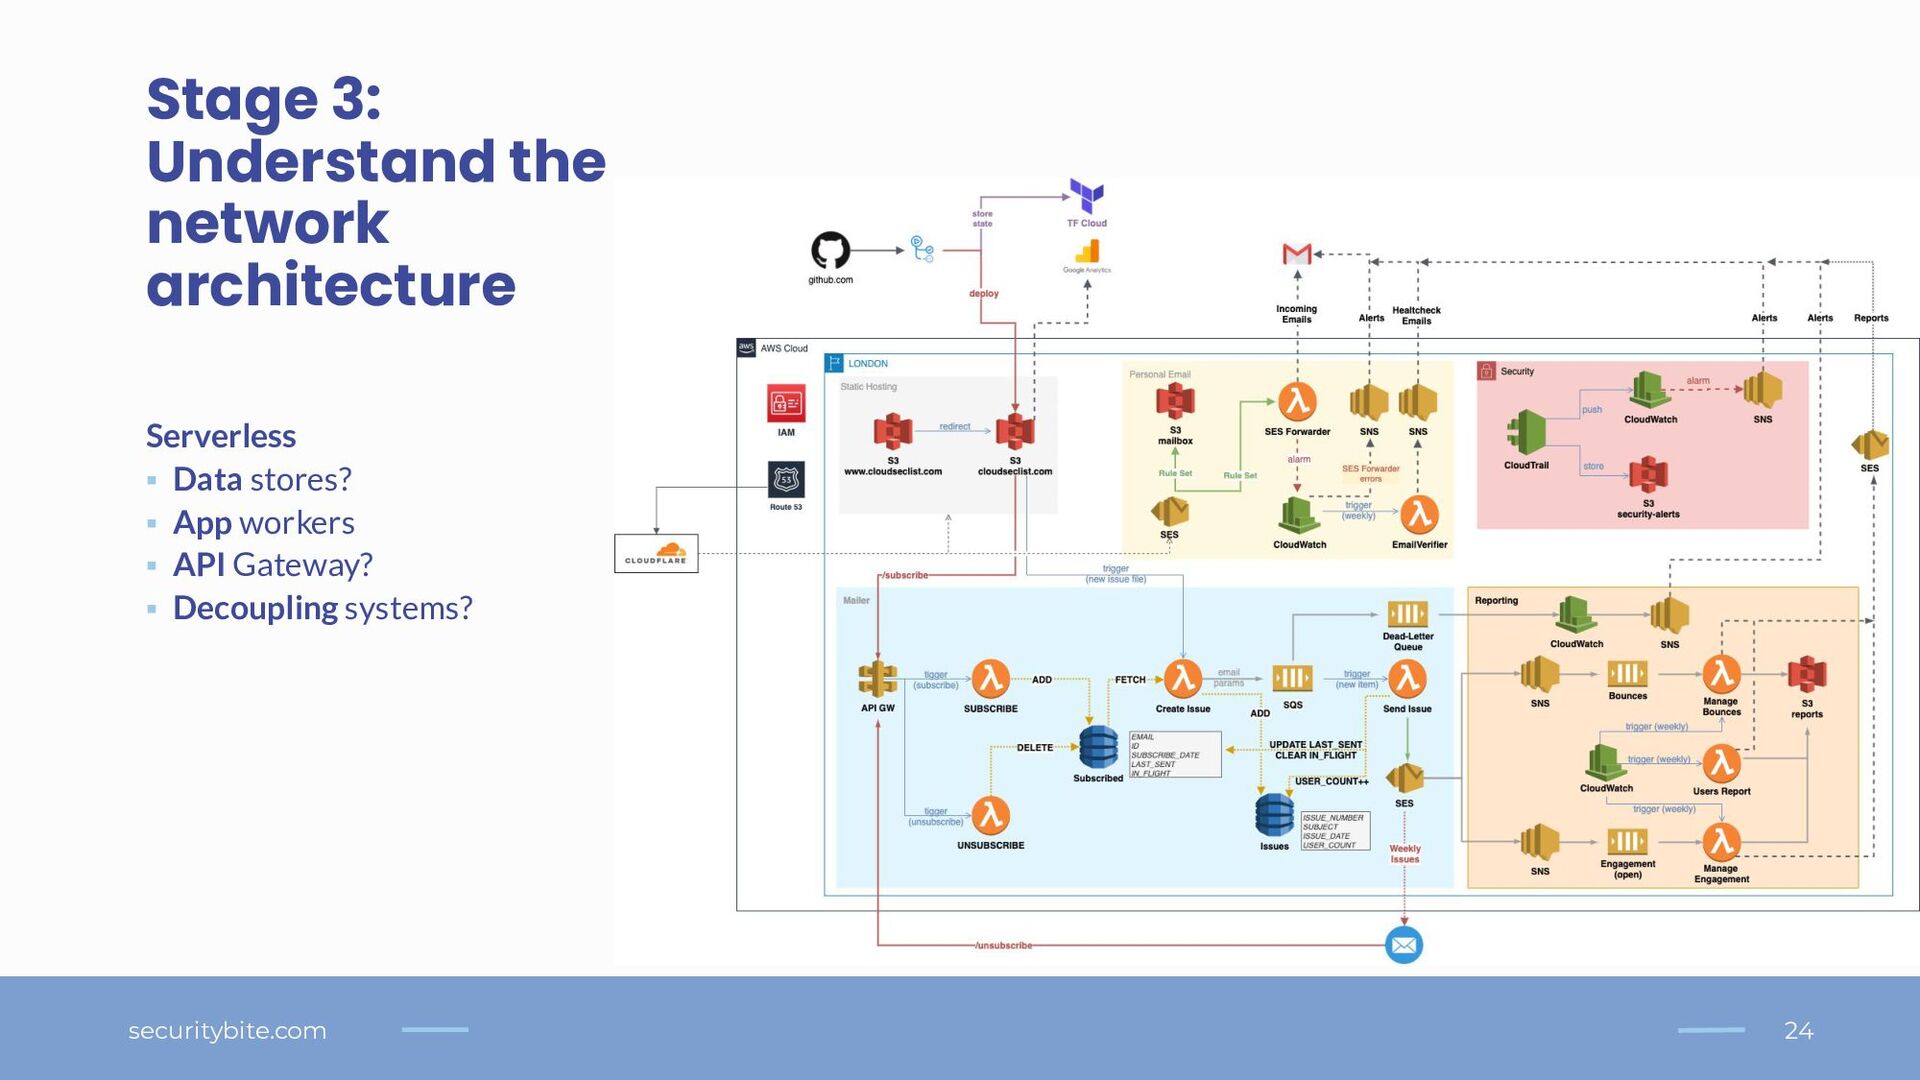
24 securitybite.com Stage 3: Understand the network architecture Serverless ▪
Data stores? ▪ App workers ▪ API Gateway? ▪ Decoupling systems? -
25 securitybite.com Stage 3: Understand the network architecture VMs ▪
Exposed to the Internet? ▪ Which OS? ▪ How are hosts hardened? ▪ How do engineers connect? ▪ Pet vs cattle? -
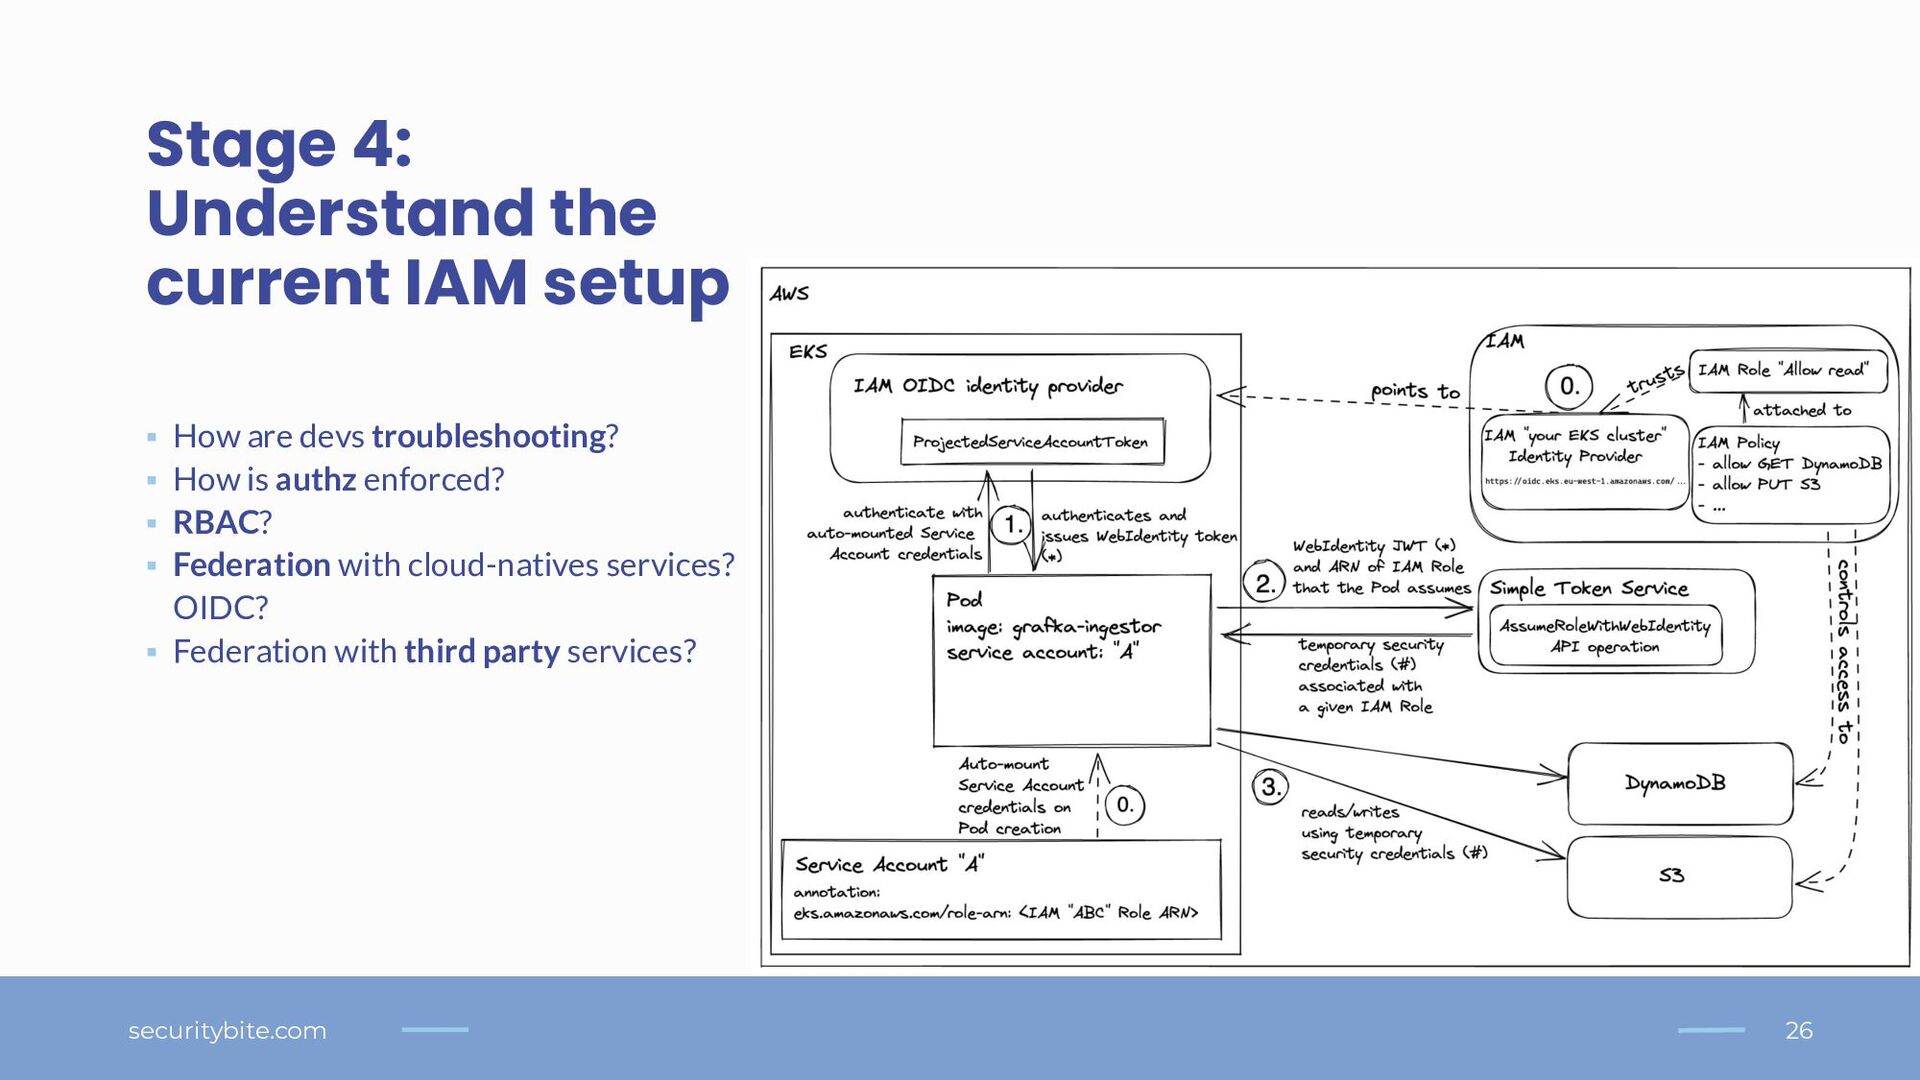
26 securitybite.com Stage 4: Understand the current IAM setup ▪
How are devs troubleshooting? ▪ How is authz enforced? ▪ RBAC? ▪ Federation with cloud-natives services? OIDC? ▪ Federation with third party services? -
27 securitybite.com Stage 5: Understand the current monitoring setup ▪
Are security-related logs collected at all? ▪ What kind of logs are being ingested? ▪ How are logs collected? ▪ Where are the logs forwarded? Kubernetes ▪ Are audit logs collected? ▪ Are System Calls and Kubernetes Audit Events collected via Falco? ▪ Is a data collector like fluentd used to collect logs? ▪ Is the data collector deployed as a Sidecar or Daemonset? -
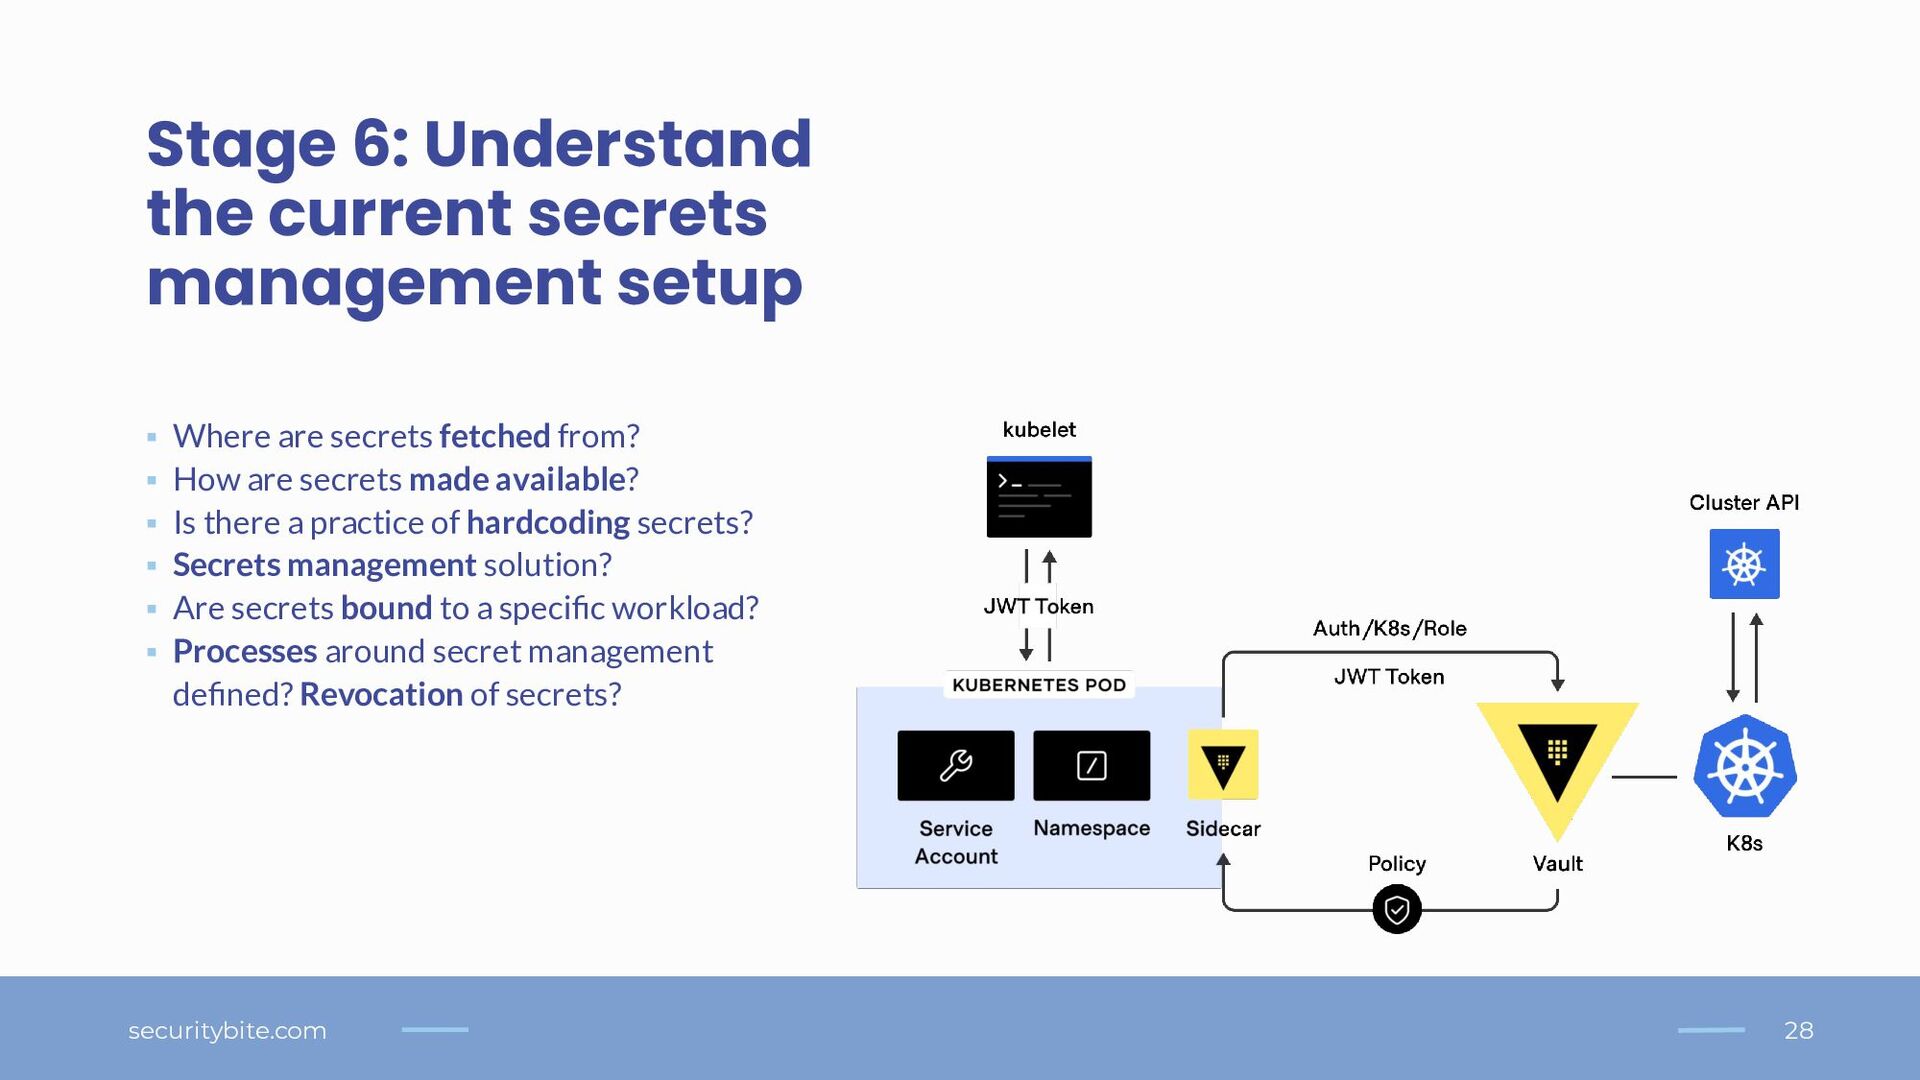
28 securitybite.com Stage 6: Understand the current secrets management setup
▪ Where are secrets fetched from? ▪ How are secrets made available? ▪ Is there a practice of hardcoding secrets? ▪ Secrets management solution? ▪ Are secrets bound to a specific workload? ▪ Processes around secret management defined? Revocation of secrets? -
29 securitybite.com Stage 7: Identify existing security controls ▪ Which
controls have already been implemented? ▪ Highly dependent on the actual workloads Stage 8: Get the low-hanging fruits ▪ Tactical scan / benchmark suite -
31 securitybite.com Stage 1: Understand the code’s structure ▪ Monorepo
vs multi-repos? ▪ CODEOWNERS? ▪ Protected branches? ▪ Code reviews via Pull Requests? ▪ Linters? ▪ Static analysis tools? ▪ Secrets detection tools? -
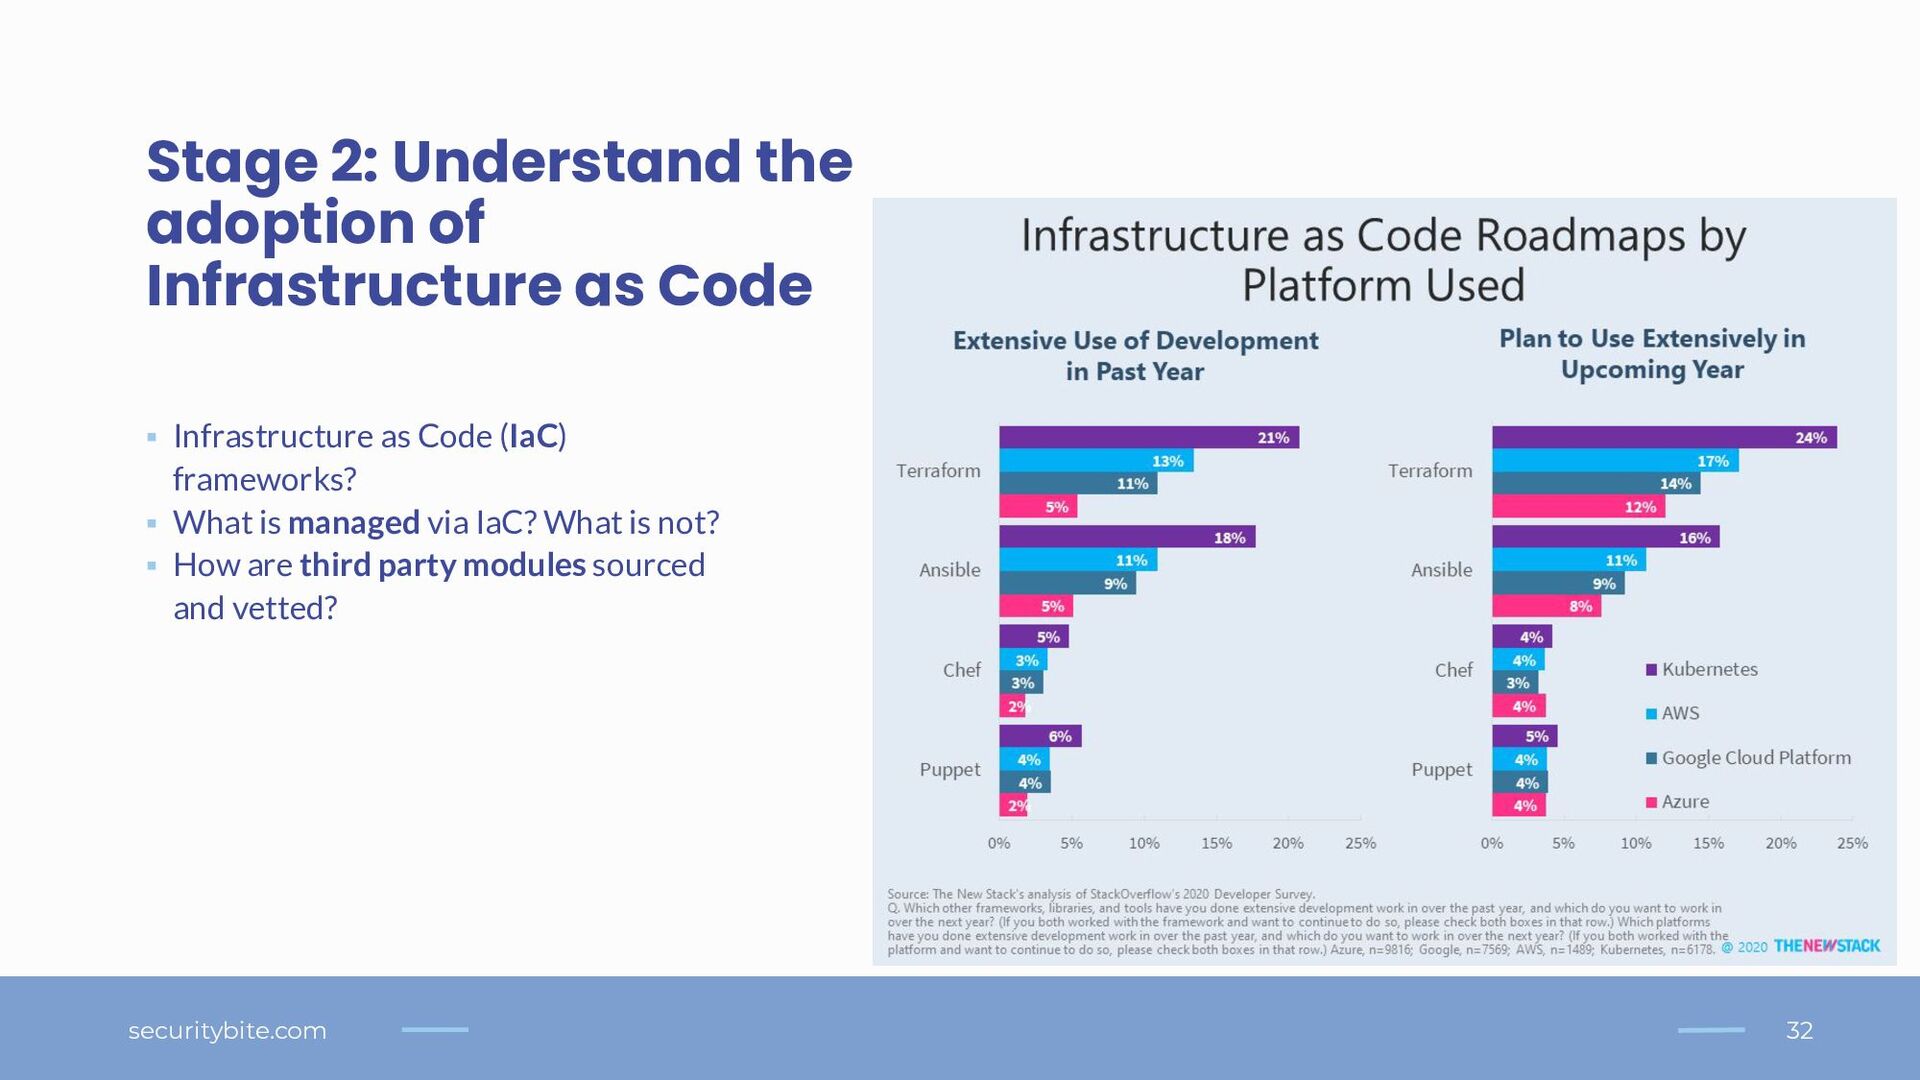
32 securitybite.com Stage 2: Understand the adoption of Infrastructure as
Code ▪ Infrastructure as Code (IaC) frameworks? ▪ What is managed via IaC? What is not? ▪ How are third party modules sourced and vetted? -
33 securitybite.com Stage 3: Understand how CI/CD is setup ▪
Which CI/CD platform? ▪ IaC deployed via CI/CD ▪ IaC tested and validated? ▪ Code provenance? ▪ Other security controls? ▪ SSDLC? -
37 securitybite.com This talk has been extracted from a (lengthy)
blog post being released today: What to look for when reviewing a company's infrastructure Place your screenshot here More on this…