Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
20171114inCyberAgent
Search
okazaki hajime
November 14, 2017
Technology
2.4k
3
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
20171114inCyberAgent
https://connpass.com/event/70903/
okazaki hajime
November 14, 2017
More Decks by okazaki hajime
See All by okazaki hajime
20220810_seccam
okazakihajime
0
160
20171222_owasp_okinawa
okazakihajime
0
930
20170218inOkinawa
okazakihajime
0
250
Other Decks in Technology
See All in Technology
AI × アーキテクト 第1・2章|生成AIの課題とアーキテクトの素養
daidaidai
1
240
書き手が人でもAIでも正しくなる道、 SREを埋め込んだDeveloper Platform / tech drivers day8
chmikata
4
640
AWSDirectConnectの構築の進め方を整理してみた
masa_my
1
170
LLM-as-a-Judgeは本当に信頼できるのか――評価器を評価する話
taka_aki
3
1.1k
クラウドサインを止めずに Nuxt へ 次の10年のために先に決めたこと
bengo4com
1
120
古い指輪から広がった JAVA コミュニティ とのつながり
yamad
0
150
CTO Night|NotionのAIエージェントとFDE
kzkhykw1991
0
310
Steerable Visual Representations
sansantech
PRO
0
360
導入から定着へ ~コーディングエージェントを日常業務に組み込む実践知~
yukisakai1225
0
220
AIをリアル世界に解き放つ 〜M5Stack×AIであなたのアイディアを手の平に〜
hamadakoji
1
450
契約で守るコンパウンドプロダクトのデザインシステム
yug1224
1
1.2k
Microsoft のサポート ライフサイクルを理解する
murachiakira
PRO
0
160
Featured
See All Featured
Taking LLMs out of the black box: A practical guide to human-in-the-loop distillation
inesmontani
PRO
3
2.5k
個人開発の失敗を避けるイケてる考え方 / tips for indie hackers
panda_program
123
22k
Joys of Absence: A Defence of Solitary Play
codingconduct
1
550
How to make the Groovebox
asonas
2
2.5k
Paper Plane
katiecoart
PRO
5
54k
Why Mistakes Are the Best Teachers: Turning Failure into a Pathway for Growth
auna
0
330
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
740
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.1k
Thoughts on Productivity
jonyablonski
76
5.4k
We Have a Design System, Now What?
morganepeng
55
8.4k
Ethics towards AI in product and experience design
skipperchong
2
440
Effective software design: The role of men in debugging patriarchy in IT @ Voxxed Days AMS
baasie
1
580
Transcript
Dockerを始めて1週間の セキュリティエンジニア 2017/11/14(Tue) CyberAgent - AdtechStudio Security okazaki hajime
自己紹介 • 氏名:岡崎 創(おかざき はじめ) • 出身:埼玉県春日部市 (クレヨンしんちゃんの街) • 職歴: ◦ 3年くらい LAMP環境のフロントエンジニア
◦ その後、3年くらい 上記のインフラエンジニア(サーバエンジニア) ◦ その後、1年くらい Webアプリケーションの脆弱性診断 ◦ その後、サイバーエージェント アドテク本部に入社( 2015/6) • 現在:アドテク本部セキュリティグループに所属
今日はコンテナ縛り?!
本日は Docker Security Beginner
Docker歴:1週間程度 • 利用したDocker version ◦ Docker version 17.09.0-ce • Dockerの登場人物
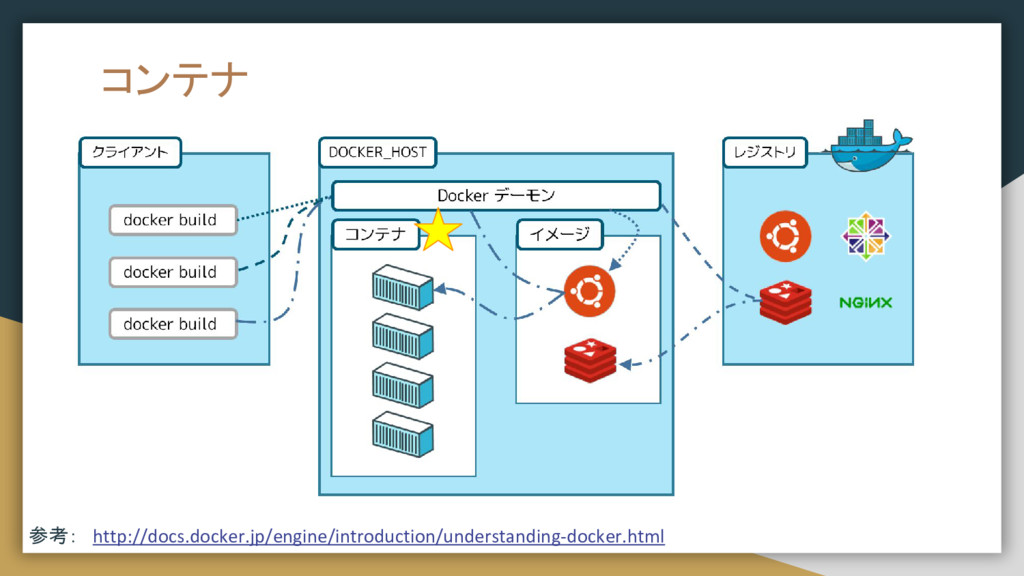
◦ クライアント、デーモン、コンテナ、イメージ、レジストリ • とりあえず、docker run をしてみた • Docker イメージの作成の仕方は、2つある? ◦ dockerfileを「使う」か「使わないか」 • 現在この程度、、、
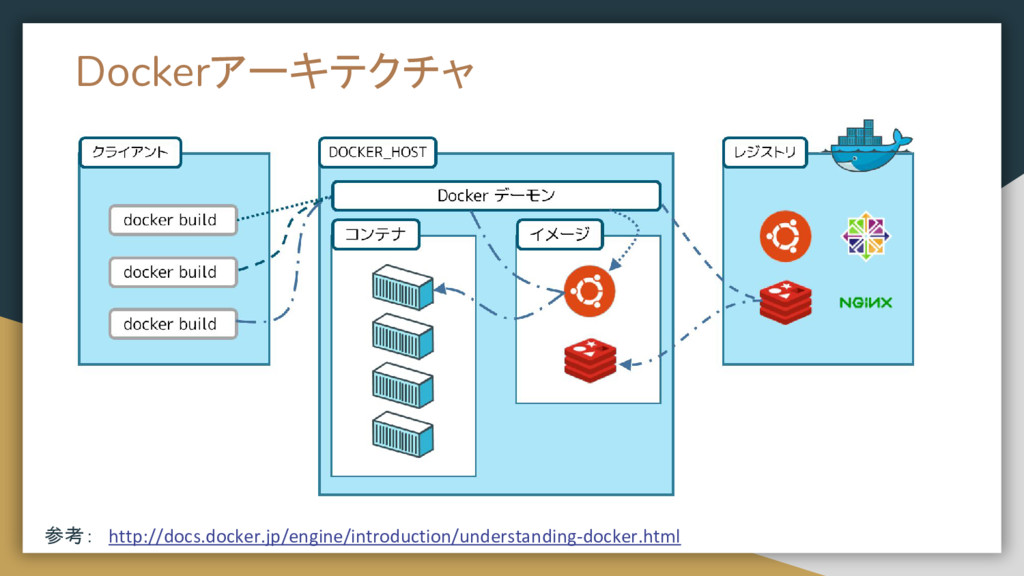
docker architecture 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html Dockerアーキテクチャ
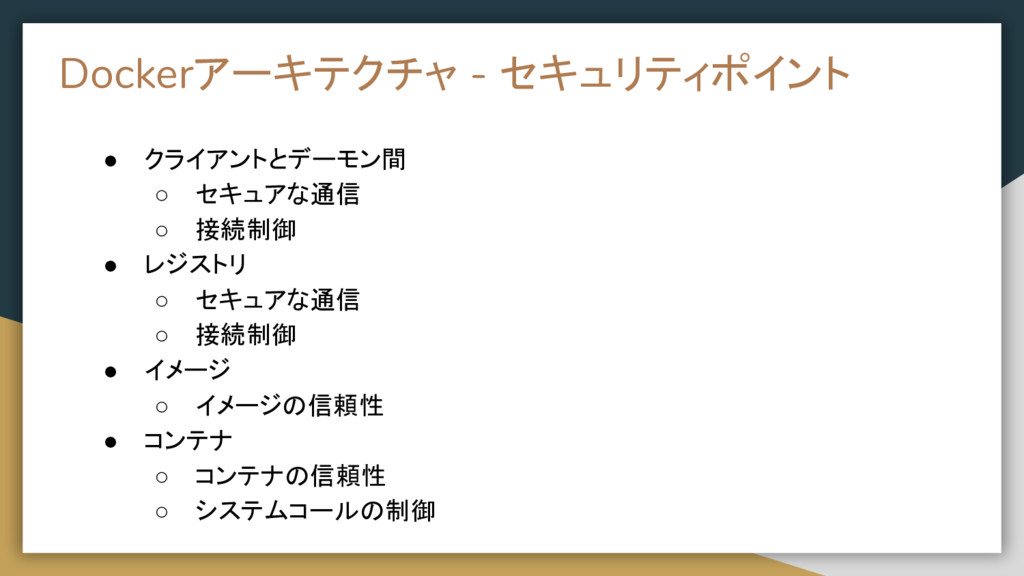
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 Dockerアーキテクチャ - セキュリティポイント
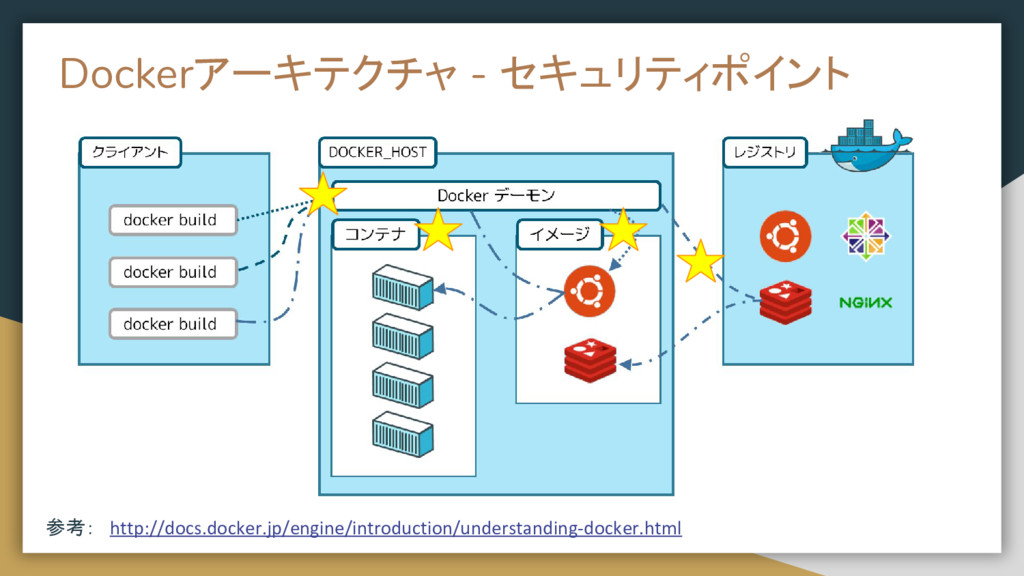
docker architecture - security point 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html Dockerアーキテクチャ - セキュリティポイント
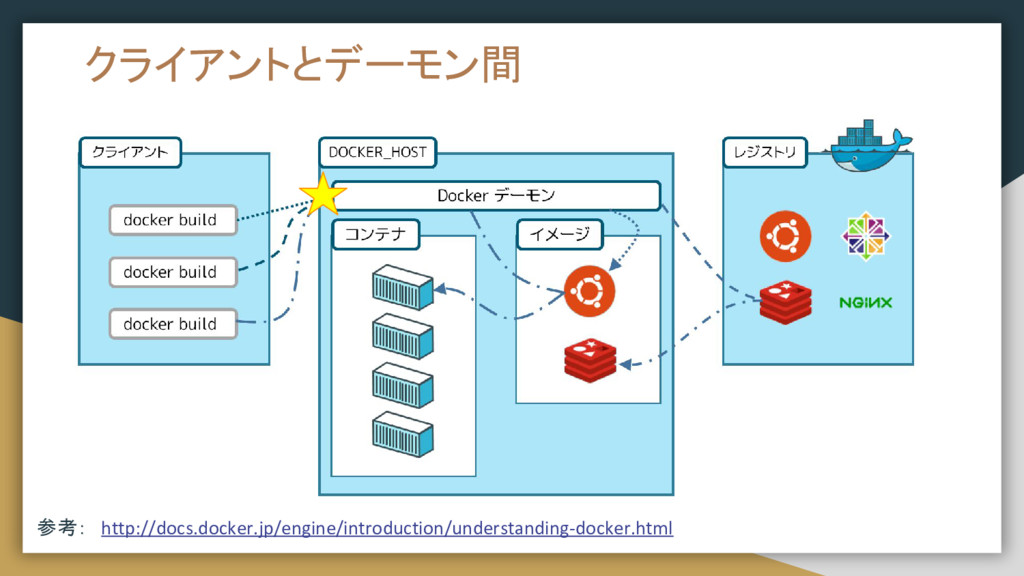
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 クライアントとデーモン間
クライアントとデーモン間 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html
クライアントとデーモン間 • TLSを利用して安全に接続しましょう • また、上記の証明書はクライアント認証にも使えます #デーモン設定に追加 $ vim /usr/lib/systemd/system/docker.service [Service]
# ExecStart=/usr/bin/dockerd ExecStart=/usr/bin/dockerd --tlsverify --tlscacert=ca.pem --tlscert=server.pem --tlskey=server-key.pem -H tcp://0.0.0.0:2376 $ systemctl daemon-reload $ systemctl restart docker
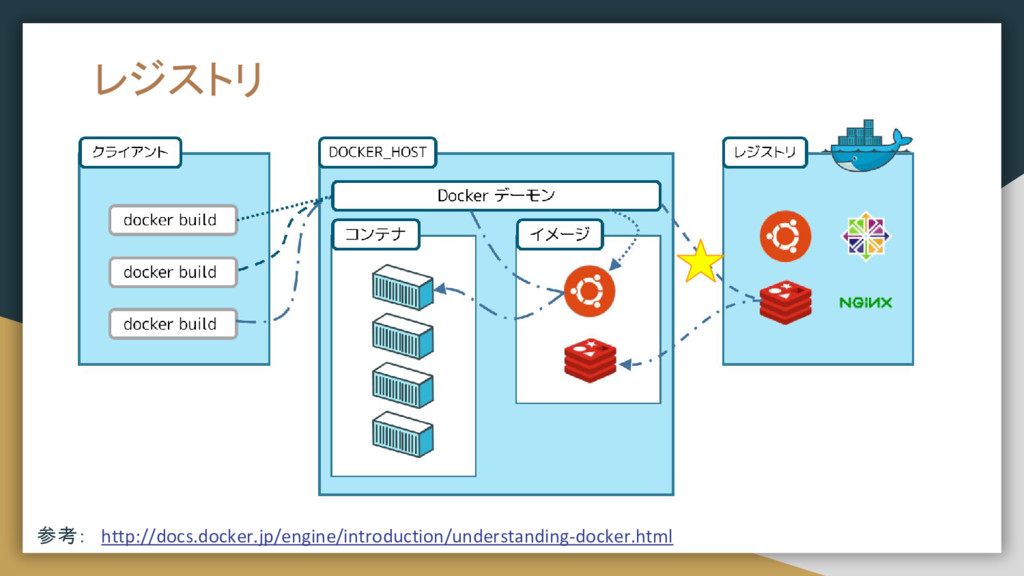
レジストリ 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 レジストリ
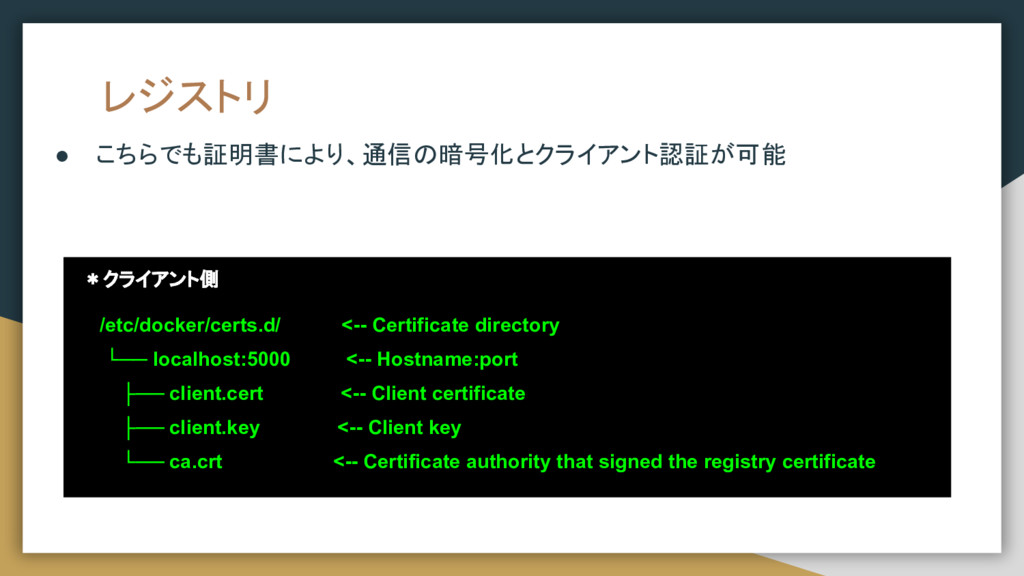
レジストリ • こちらでも証明書により、通信の暗号化とクライアント認証が可能 *クライアント側 /etc/docker/certs.d/ <-- Certificate directory └── localhost:5000
<-- Hostname:port ├── client.cert <-- Client certificate ├── client.key <-- Client key └── ca.crt <-- Certificate authority that signed the registry certificate
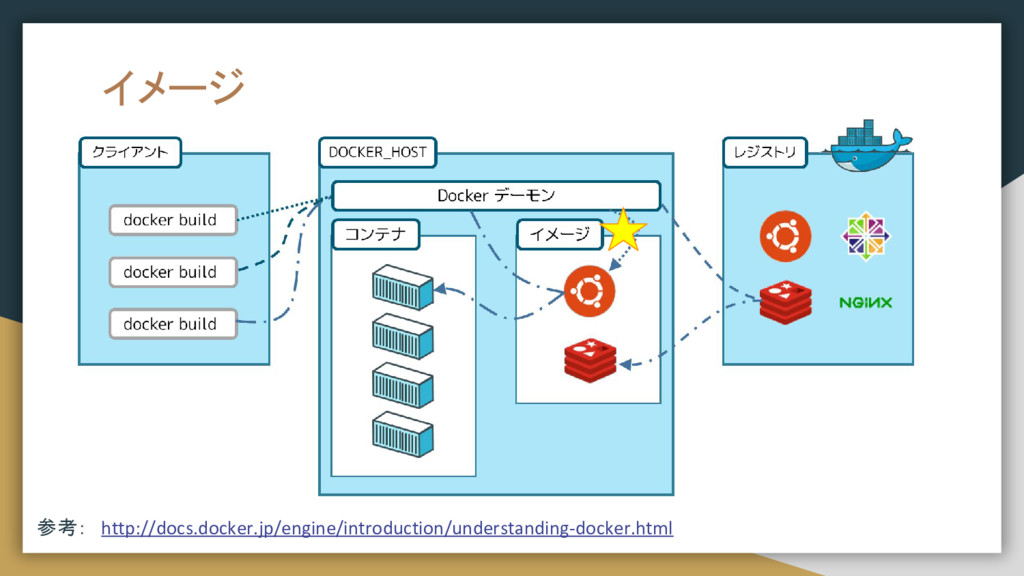
イメージ 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 イメージ
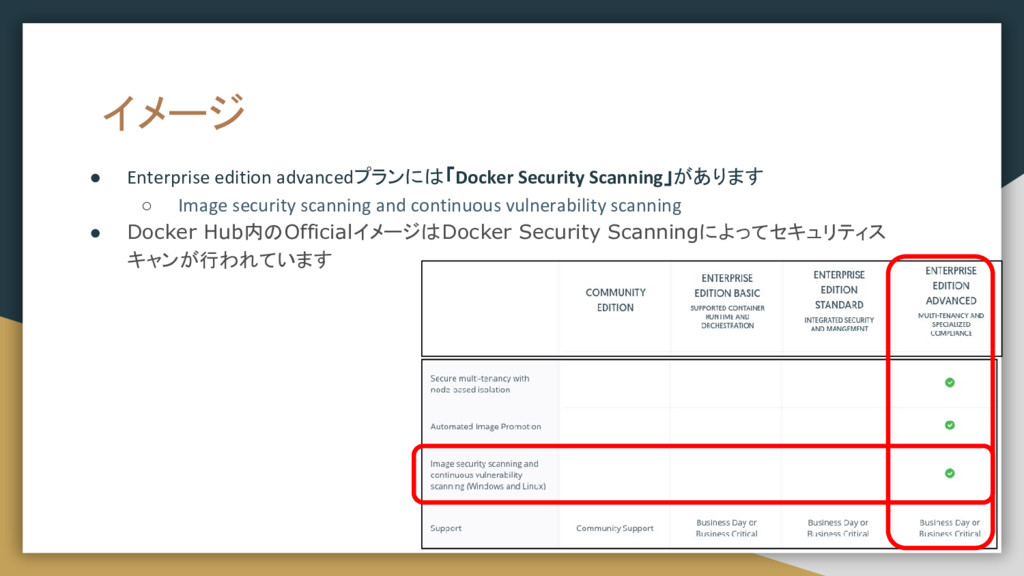
イメージ • Enterprise edition advancedプランには「Docker Security Scanning」があります ◦ Image security
scanning and continuous vulnerability scanning • Docker Hub内のOfficialイメージはDocker Security Scanningによってセキュリティス キャンが行われています
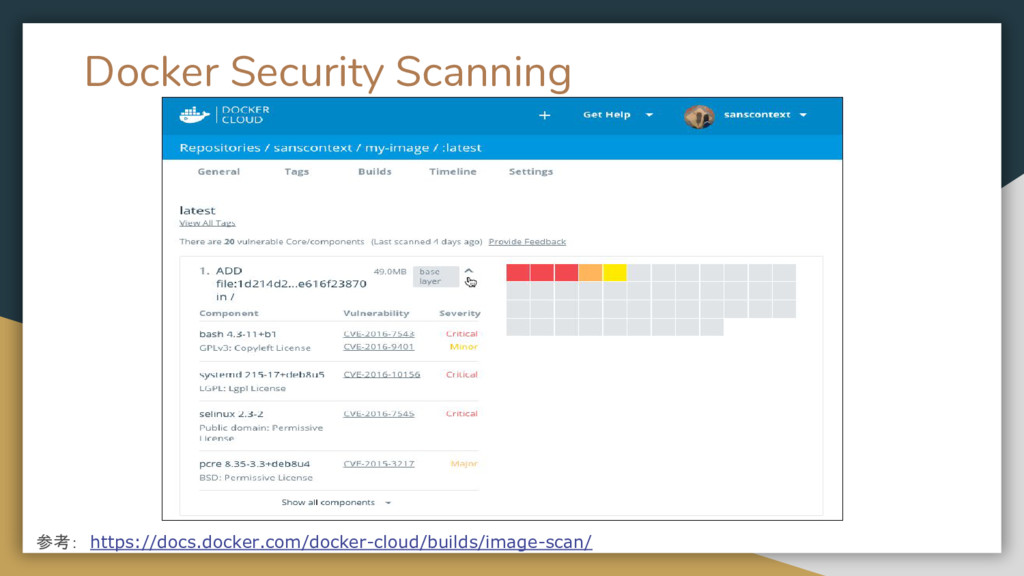
Docker Security Scanning CVE(Common Vulnerabilities and Exposures):脆弱性情報データベースと連動 参考: https://success.docker.com/Architecture/Docker_Reference_Architecture%3A_Securing_Docker_EE_and_Security_Best_Practices
Docker Security Scanning 参考: https://docs.docker.com/docker-cloud/builds/image-scan/
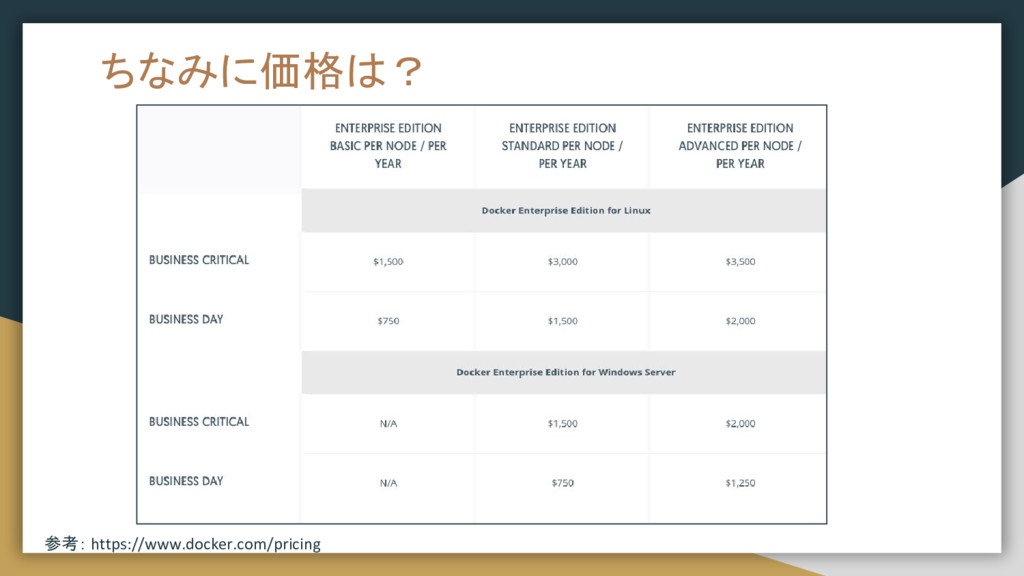
ちなみに価格は? 参考: https://www.docker.com/pricing
コンテナ 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 コンテナ
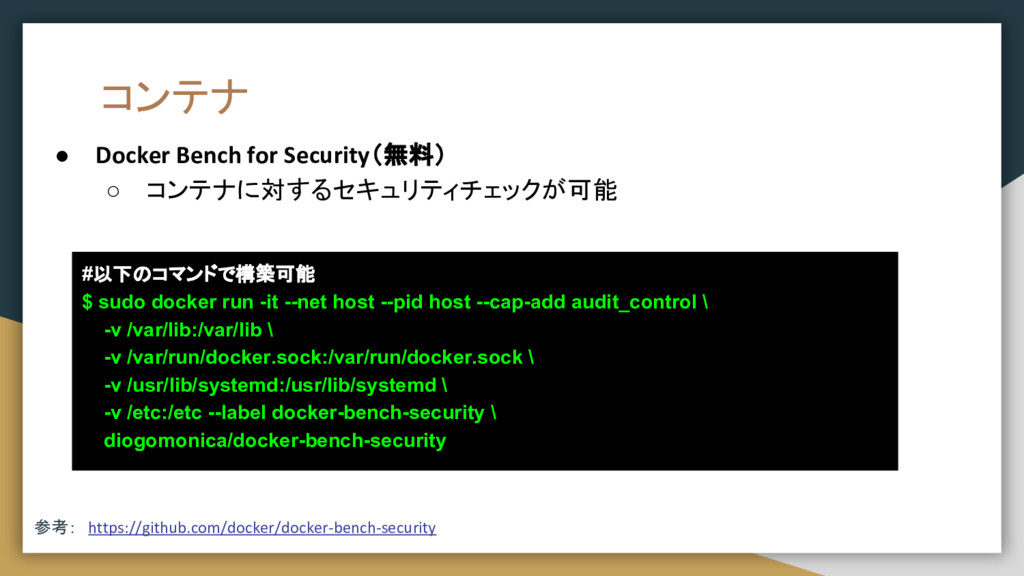
コンテナ • Docker Bench for Security(無料) ◦ コンテナに対するセキュリティチェックが可能 #以下のコマンドで構築可能 $
sudo docker run -it --net host --pid host --cap-add audit_control \ -v /var/lib:/var/lib \ -v /var/run/docker.sock:/var/run/docker.sock \ -v /usr/lib/systemd:/usr/lib/systemd \ -v /etc:/etc --label docker-bench-security \ diogomonica/docker-bench-security 参考: https://github.com/docker/docker-bench-security
無料!?
Docker Bench for Security *チェック項目 [INFO] 1 - Host Configuration
[INFO] 2 - Docker Daemon Configuration [INFO] 3 - Docker Daemon Configuration Files [INFO] 4 - Container Images and Build Files [INFO] 5 - Container Runtime [INFO] 6 - Docker Security Operations *結果 [INFO] 4 - Container Images and Build Files [WARN] 4.1 - Create a user for the container [WARN] * Running as root: vibrant_bassi [WARN] * Running as root: mysql [WARN] * Running as root: php ー> コンテナがrootユーザで動作しているため、警告!
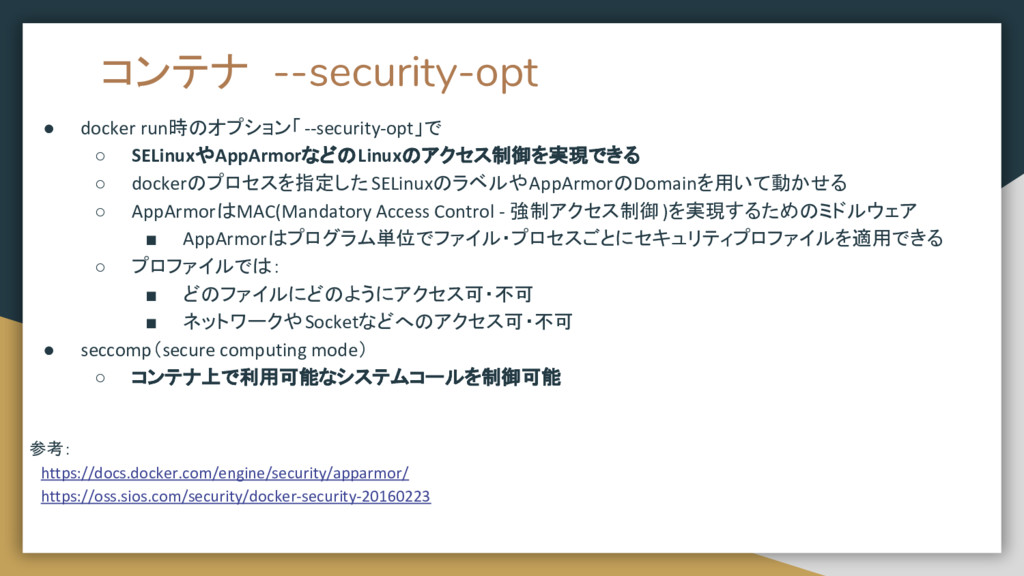
コンテナ --security-opt • docker run時のオプション「--security-opt」で ◦ SELinuxやAppArmorなどのLinuxのアクセス制御を実現できる ◦ dockerのプロセスを指定した SELinuxのラベルやAppArmorのDomainを用いて動かせる
◦ AppArmorはMAC(Mandatory Access Control - 強制アクセス制御)を実現するためのミドルウェア ▪ AppArmorはプログラム単位でファイル・プロセスごとにセキュリティプロファイルを適用できる ◦ プロファイルでは: ▪ どのファイルにどのようにアクセス可・不可 ▪ ネットワークやSocketなどへのアクセス可・不可 • seccomp(secure computing mode) ◦ コンテナ上で利用可能なシステムコールを制御可能 参考: https://docs.docker.com/engine/security/apparmor/ https://oss.sios.com/security/docker-security-20160223
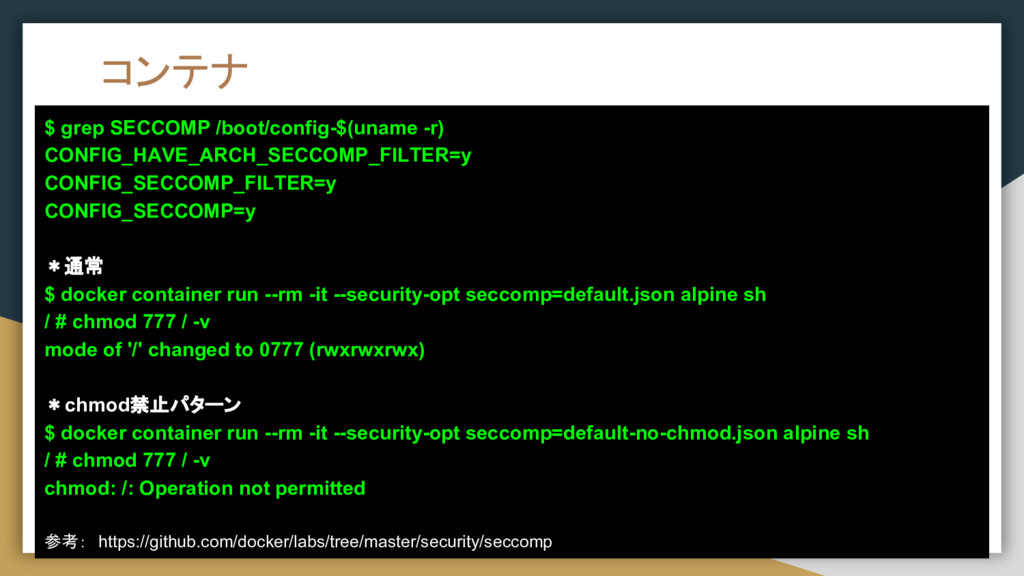
コンテナ $ grep SECCOMP /boot/config-$(uname -r) CONFIG_HAVE_ARCH_SECCOMP_FILTER=y CONFIG_SECCOMP_FILTER=y CONFIG_SECCOMP=y *通常
$ docker container run --rm -it --security-opt seccomp=default.json alpine sh / # chmod 777 / -v mode of '/' changed to 0777 (rwxrwxrwx) *chmod禁止パターン $ docker container run --rm -it --security-opt seccomp=default-no-chmod.json alpine sh / # chmod 777 / -v chmod: /: Operation not permitted 参考: https://github.com/docker/labs/tree/master/security/seccomp
このあたりは、よくわからない 今後の課題
Understanding Docker Security and Best Practices 参考: https://blog.docker.com/2015/05/understanding-docker-security-and- best-practices/ DOCKER
SECURITY blog https://www.docker.com/docker-security
ご清聴 ありがとうございました


 okazakihajime
 daidaidai
 chmikata
 masa_my
 taka_aki
 bengo4com
 yamad
 kzkhykw1991
 sansantech
 yukisakai1225
 hamadakoji
 yug1224
 murachiakira
 inesmontani
 panda_program
 codingconduct
 asonas
 katiecoart
 auna
 baasie
 reverentgeek
 jonyablonski
 morganepeng
 skipperchong