Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
XSS with HTML parsing confusion #appsecapac2014
Search
OWASP Japan
March 20, 2014
1.3k
4
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
XSS with HTML parsing confusion #appsecapac2014
OWASP Japan
March 20, 2014
More Decks by OWASP Japan
See All by OWASP Japan
OWASP Night 2019.03 Tokyo
owaspjapan
0
420
OWASP SAMMを活用したセキュア開発の推進
owaspjapan
0
1.1k
20190107_AbuseCaseCheatSheet
owaspjapan
0
230
セキュリティ要求定義で使える非機能要求グレードとASVS
owaspjapan
5
1.2k
AWSクラスタに捧ぐウェブを衛っていく方法論と死なない程度の修羅場の価値
owaspjapan
9
3.6k
Shifting Left Like a Boss
owaspjapan
2
350
OWASP Top 10 and Your Web Apps
owaspjapan
2
450
OWASP Japan Proposal: Encouraging Japanese Translation
owaspjapan
1
310
elegance_of_OWASP_Top10_2017
owaspjapan
2
590
Featured
See All Featured
Writing Fast Ruby
sferik
630
63k
Why Mistakes Are the Best Teachers: Turning Failure into a Pathway for Growth
auna
0
280
New Earth Scene 8
popppiees
3
2.5k
The SEO Collaboration Effect
kristinabergwall1
1
550
My Coaching Mixtape
mlcsv
0
310
Templates, Plugins, & Blocks: Oh My! Creating the theme that thinks of everything
marktimemedia
31
2.9k
Stop Working from a Prison Cell
hatefulcrawdad
274
21k
JAMstack: Web Apps at Ludicrous Speed - All Things Open 2022
reverentgeek
1
590
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.2k
The Invisible Side of Design
smashingmag
301
52k
The untapped power of vector embeddings
frankvandijk
2
1.9k
Skip the Path - Find Your Career Trail
mkilby
1
230
Transcript
XSS with HTML parsing confusion XSS with HTML parsing confusion
ma.la 2014-03-20
Today's theme Today's theme XSS with HTML parsing issue Be
related especially with a WYSIWYG editor.
The beginning The beginning I found and reported JavaScript execution
on HTML mail. Sparrow, Mailbox, NAVER mail
Example: Mailbox's case Example: Mailbox's case Mailbox.app Javascript execution They
restrict script by server-side. I've report another XSS vector. http://miki.it/blog/2013/9/24/mailboxapp-javascript- execution/
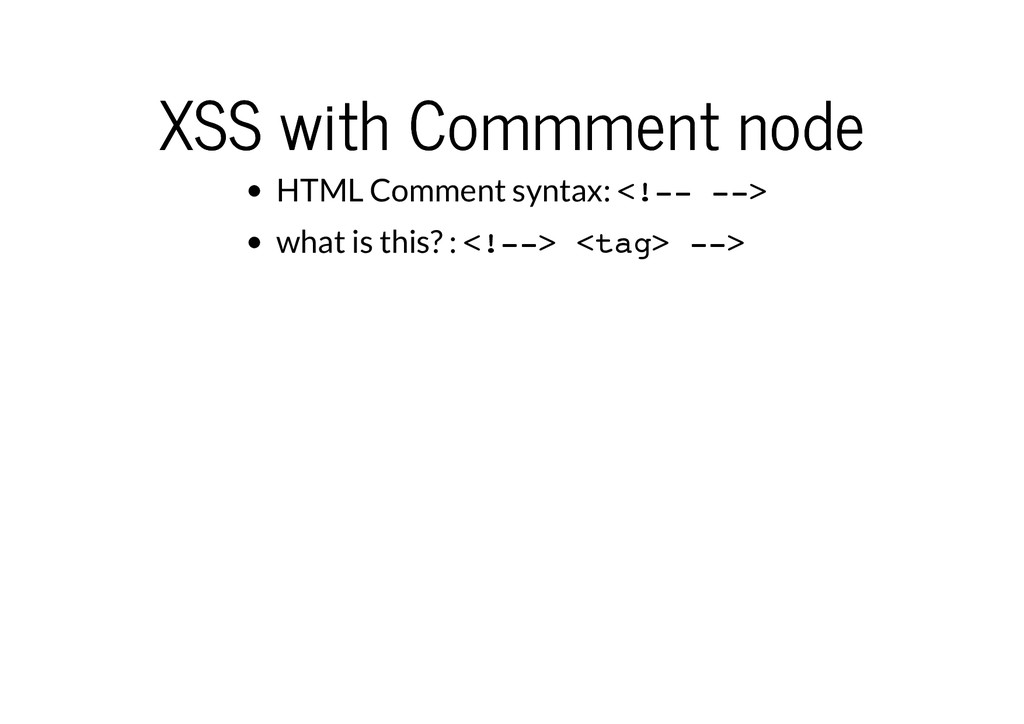
XSS with Commment node XSS with Commment node HTML Comment
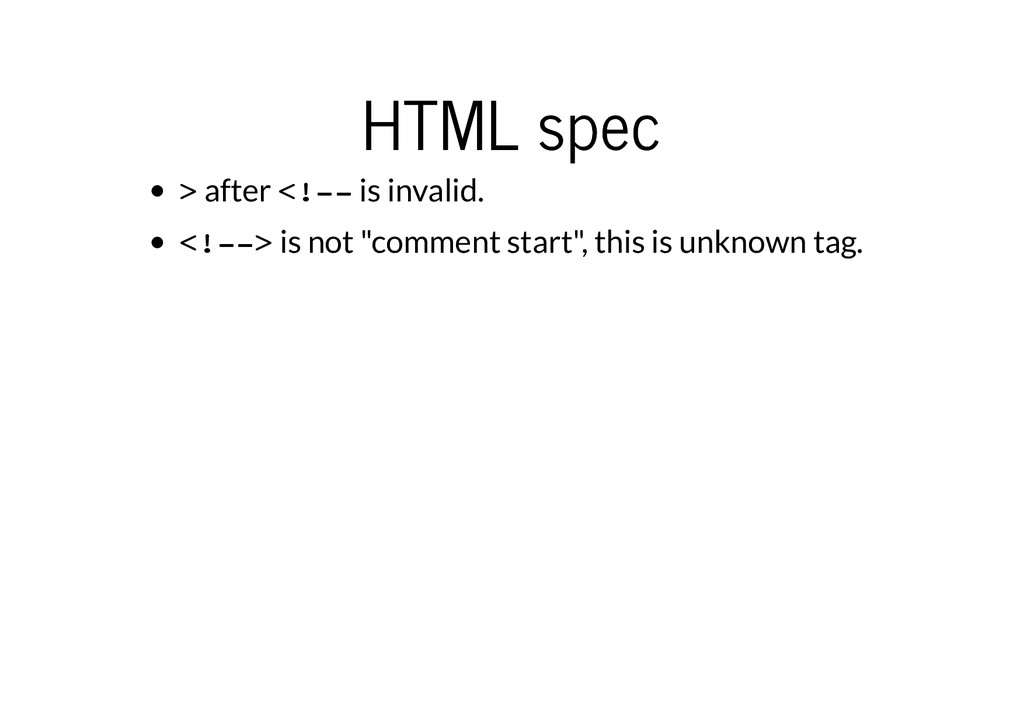
syntax: <!-- --> what is this? : <!--> <tag> -->
HTML spec HTML spec > after <!-- is invalid. <!-->
is not "comment start", this is unknown tag.
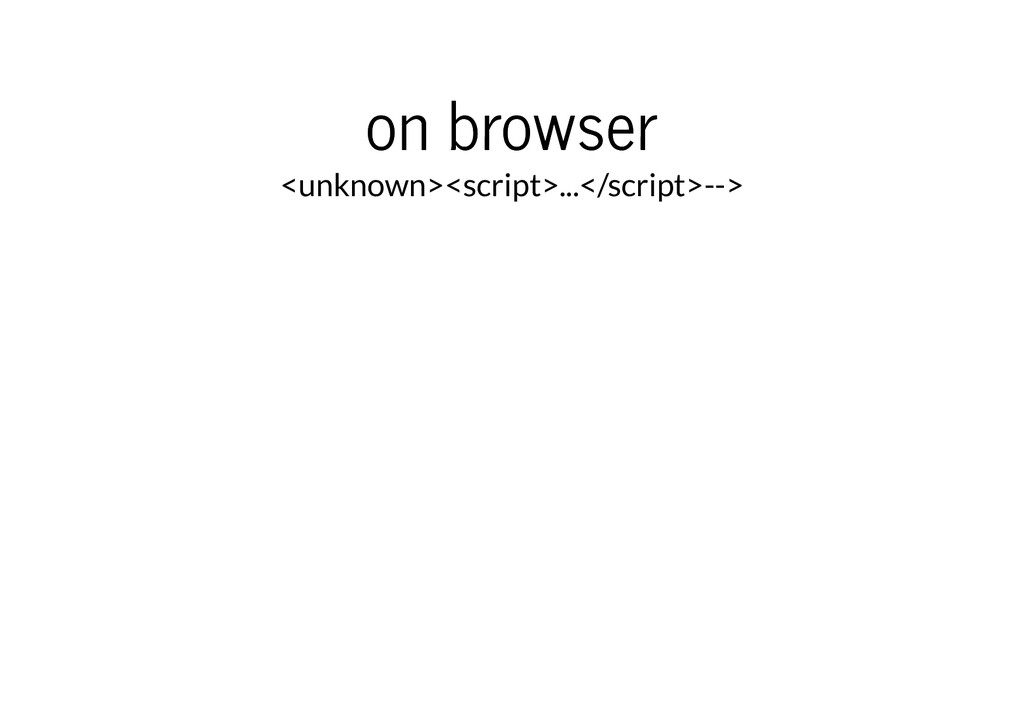
on browser on browser <unknown><script>...</script>-->
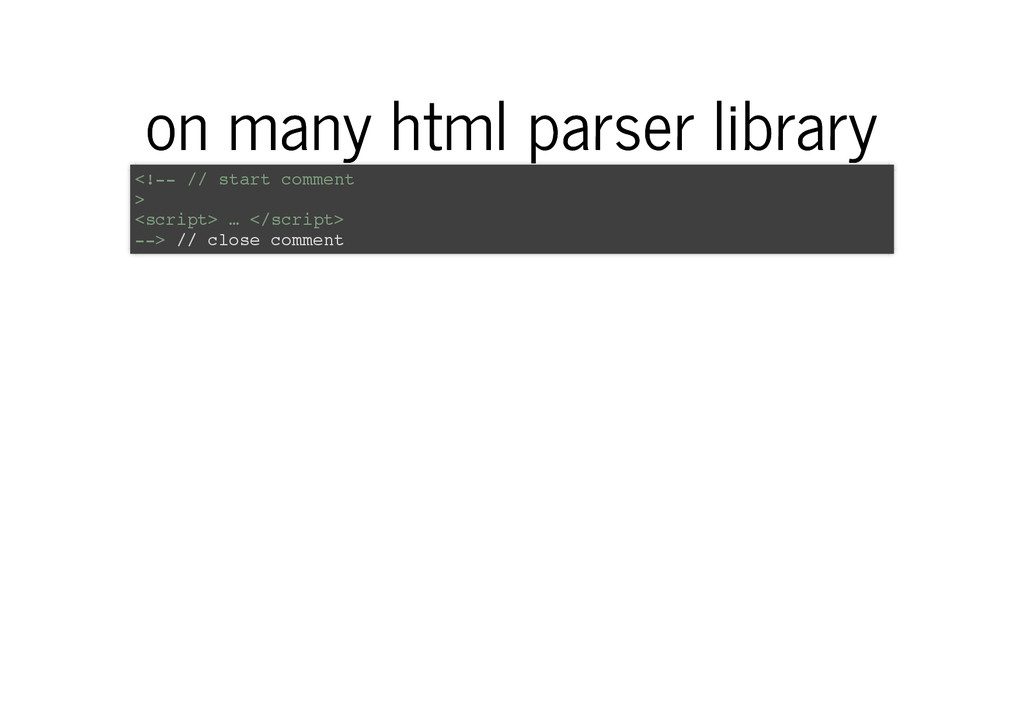
on many html parser library on many html parser library
<!-- // start comment > <script> … </script> --> // close comment
HTML "Comment node" is safe? HTML "Comment node" is safe?
NO!
conditional comments for IE conditional comments for IE <!--[if IE]>
HTML <![endif]-->
I found XSS on many CMS I found XSS on
many CMS It is not known so much? WYSIWYG editor / TinyMCE Some CMS restrict HTML tag by server-side filter.
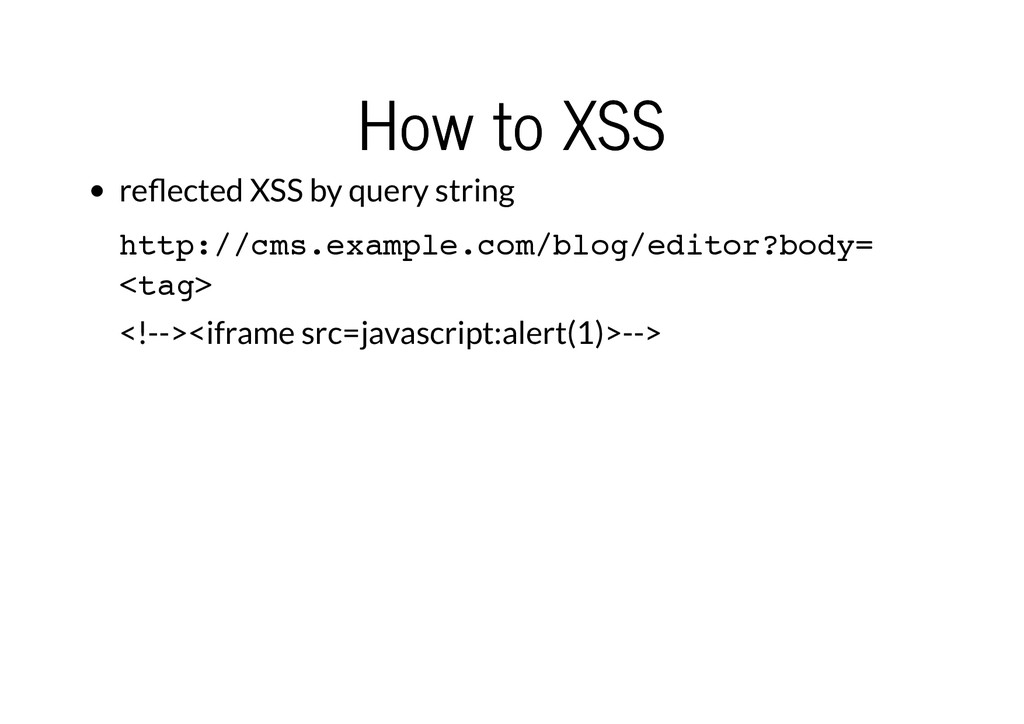
How to XSS How to XSS reflected XSS by query
string http://cms.example.com/blog/editor?body= <tag> <!--><iframe src=javascript:alert(1)>-->
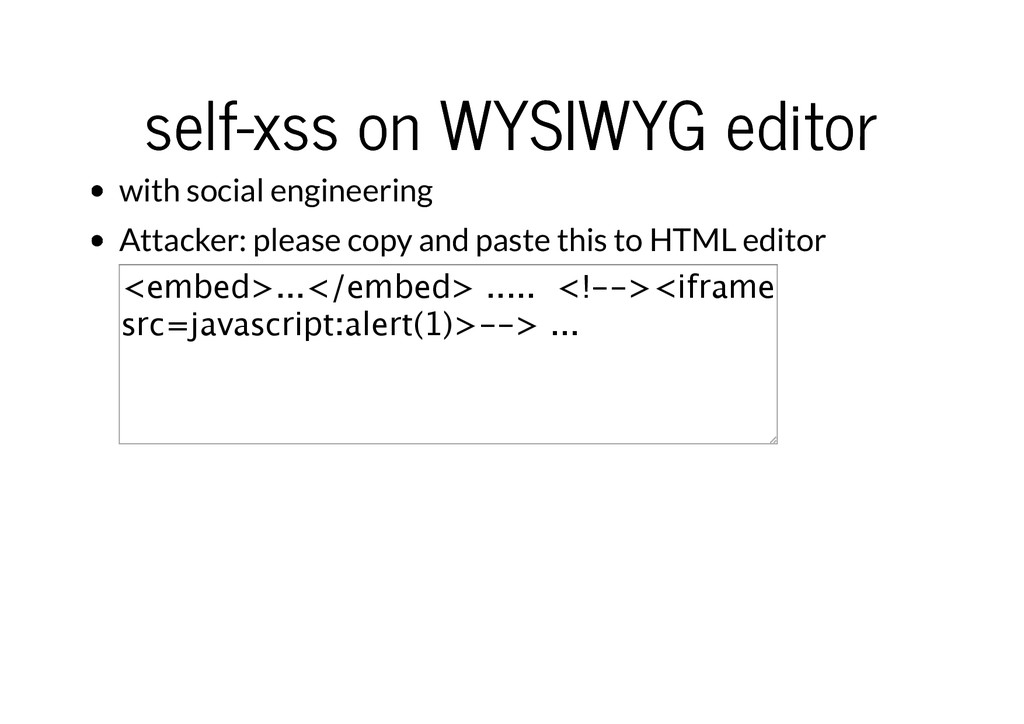
self-xss on WYSIWYG editor self-xss on WYSIWYG editor with social
engineering Attacker: please copy and paste this to HTML editor <embed>...</embed> ..... <!--><iframe src=javascript:alert(1)>--> ...
TinyMCE TinyMCE TinyMCE can restrict tag and attribute by "valid_elements"
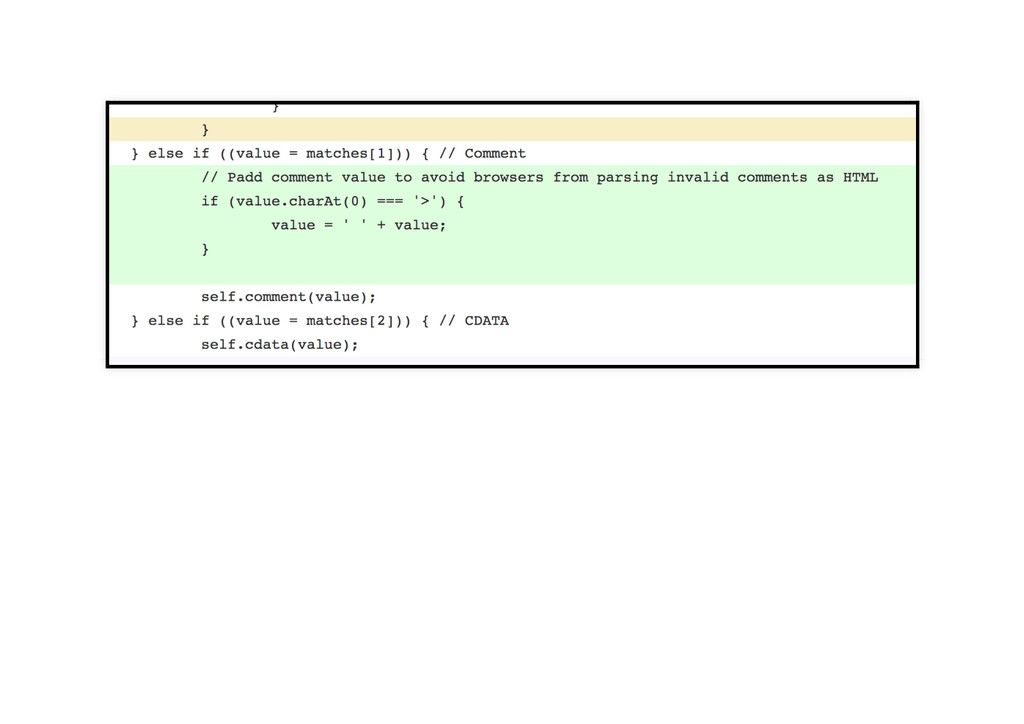
option. This is client-side filter by JavaScript. if you permit a comment tag, ALL tags are permitted. I've report this problem to TinyMCE.
TinyMCE TinyMCE now fixed https://github.com/tinymce/tinymce/commit/22374b5d4aec47487 e99a63d5854e2e7de55719d496c752a2
None
Example Example XSS or self-XSS
WordPress WordPress XSS on editor page only in wordpress.com, not
wordpress.org reported: 2013-9-30, and now fixed
Movable Type Movable Type XSS on editor page reported: 2013-9-30,
fixed on MT6 and
Google Blogger Google Blogger Self XSS on editor page white
list filter bypass via <!--> reported: 2013-10-2, now fixed, $500
Common pattern Common pattern preview function + raw HTML editor,
embed code, etc self-XSS was possible in some case (server-side filter is useless for self DOM XSS)
How to fix #1 How to fix #1 simply, output
valid html use whitelist, output wellformed valid html
How to fix #2 How to fix #2 use browser's
parser you don't need to write new HTML parser. document.implementation.createHTMLDocument some_element.innerHTML = htmlstring ↑ execute <img src=x onerror=...> createHTMLDocument do only parsing, create dead DOM node.
Opera12 Opera12 Opera12's createHTMLDocument is buggy, don't use it. Opera12
execute <img src=x onerror=...>
Conclusions Conclusions There is difference between actual browser and js/server-
side HTML parser. invalid html causes the problem which is not predicted. use whitelist, output wellformed valid html.


 owaspjapan
 sferik
 auna
 popppiees
 kristinabergwall1
 mlcsv
 marktimemedia
 hatefulcrawdad
 reverentgeek
 tomoyanonymous
 smashingmag
 frankvandijk
 mkilby