Share
Embed
What Healthcare Can Learn From Interesting Directions in IoT Security
Short presentation given at Archimedes Workshop on Medical Device Security 2016
Zach Lanier
May 16, 2016
Transcript
51 slides
-
What Healthcare Can Learn from Interesting Directions in IoT Security
ZACH LANIER Director of Research -
What Healthcare Can Learn from Interesting Directions in IoT Security
ZACH LANIER Director of Research (a.k.a IDIoTS) -
Who is this clown? • Zach Lanier • Director of
Research, Cylance • Old net, web/app, mobile/ embedded security research/ pen test type • Previously at Accuvant Labs and Duo Security • Co-author, "Android Hacker's Handbook" (Wiley, April 2014) -
Agenda • Challenges Faced • Some “Lessons” • Field Innovations
(?) in IoT Security • Solutions “we” would like to see • Case Studies / Predictions • Q&A -
About the Internet of Things • “The Internet of Things
is the network of physical objects that contain embedded technology to communicate and sense or interact with their internal states or the external environment.” (Gartner IT Glossary) • “Machine to machine (M2M) refers to technologies that allow both wireless and wired systems to communicate with other devices of the same type.” • IoT Growth Estimates • Gartner: 26 billion units by 2020 • ABI Research: 30 billion units by 2020 -
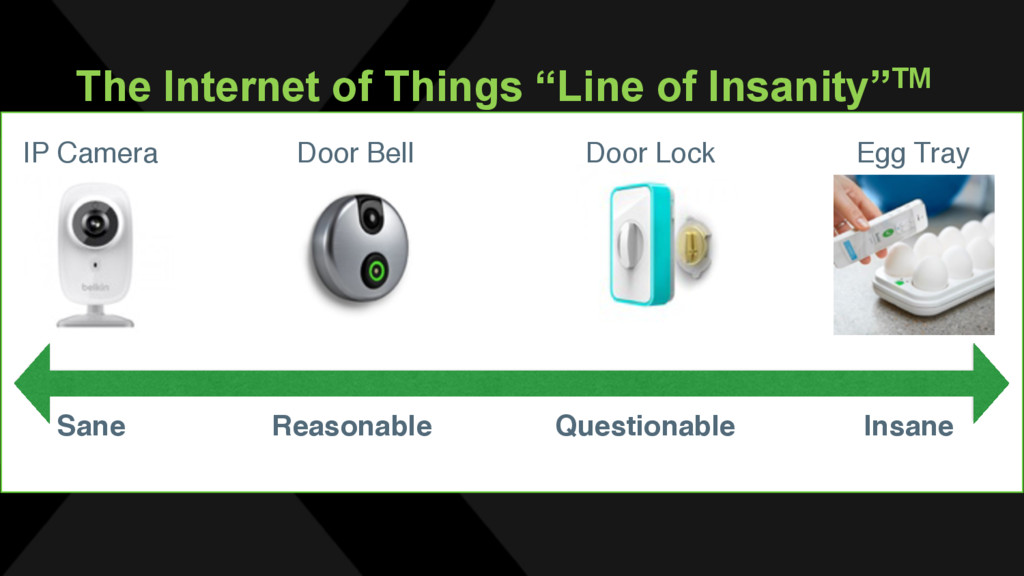
The Internet of Things “Line of Insanity”TM Sane Reasonable Insane
Questionable Egg Tray IP Camera Door Lock Door Bell -
Challenges: “Process” • Verification of healthcare professionals' credentials • (i.e.
"are you actually a doctor?") • Rights / privileges (technical) should be predicated on these credentials, such as "STOP HEART COMMAND” -
Challenges: “Technology” • Hardware • Ensuring integrity / trustworthiness of
code (limited execution environment / power consumption / clock speed) • Flashing devices • Can be convoluted process • Emergency situations => need immediate access • Backend/software challenges • Security of supporting infrastructure • Web services • Communications channels -
Challenges: “User Awareness/Behavior” • Users may not know how to
update device firmware or apps • If that’s even a capability • Disparity in management: web console v. mobile app v. physical “update” button • Lack of feedback or notification for updates or errors • How does a user know their IoT or medical device was updated or, worse, compromised? -
Example: Basic Hardware Security + = + Least common denominator:
Logic analyzer Bus Pirate UART headers Console! -
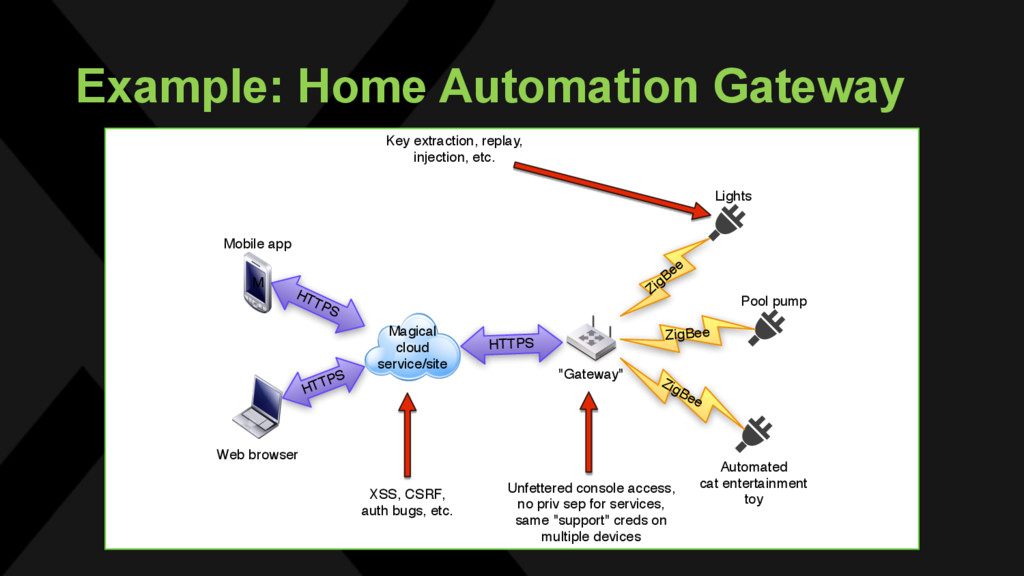
Example: Home Automation Gateway Magical cloud service/site M ZigBee ZigBee
ZigBee HTTPS HTTPS HTTPS Mobile app Web browser "Gateway" Lights Pool pump Automated cat entertainment toy XSS, CSRF, auth bugs, etc. Key extraction, replay, injection, etc. Unfettered console access, no priv sep for services, same "support" creds on multiple devices -
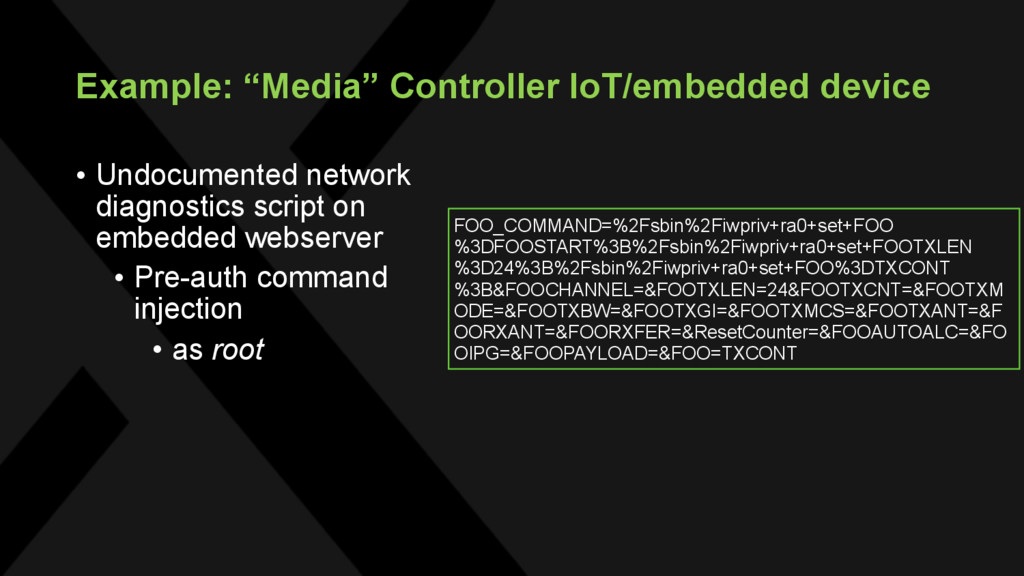
Example: “Media” Controller IoT/embedded device • Undocumented network diagnostics script
on embedded webserver • Pre-auth command injection -
Example: “Media” Controller IoT/embedded device • Undocumented network diagnostics script
on embedded webserver • Pre-auth command injection • as root -
Example: “Media” Controller IoT/embedded device • Undocumented network diagnostics script
on embedded webserver • Pre-auth command injection • as root FOO_COMMAND=%2Fsbin%2Fiwpriv+ra0+set+FOO %3DFOOSTART%3B%2Fsbin%2Fiwpriv+ra0+set+FOOTXLEN %3D24%3B%2Fsbin%2Fiwpriv+ra0+set+FOO%3DTXCONT %3B&FOOCHANNEL=&FOOTXLEN=24&FOOTXCNT=&FOOTXM ODE=&FOOTXBW=&FOOTXGI=&FOOTXMCS=&FOOTXANT=&F OORXANT=&FOORXFER=&ResetCounter=&FOOAUTOALC=&FO OIPG=&FOOPAYLOAD=&FOO=TXCONT -
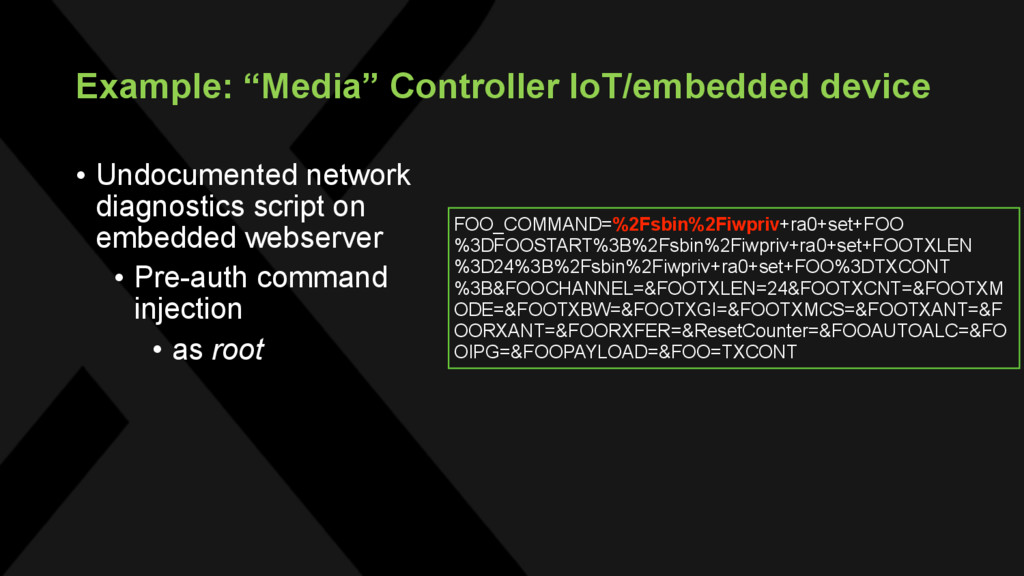
Example: “Media” Controller IoT/embedded device • Undocumented network diagnostics script
on embedded webserver • Pre-auth command injection • as root FOO_COMMAND=%2Fsbin%2Fiwpriv+ra0+set+FOO %3DFOOSTART%3B%2Fsbin%2Fiwpriv+ra0+set+FOOTXLEN %3D24%3B%2Fsbin%2Fiwpriv+ra0+set+FOO%3DTXCONT %3B&FOOCHANNEL=&FOOTXLEN=24&FOOTXCNT=&FOOTXM ODE=&FOOTXBW=&FOOTXGI=&FOOTXMCS=&FOOTXANT=&F OORXANT=&FOORXFER=&ResetCounter=&FOOAUTOALC=&FO OIPG=&FOOPAYLOAD=&FOO=TXCONT -
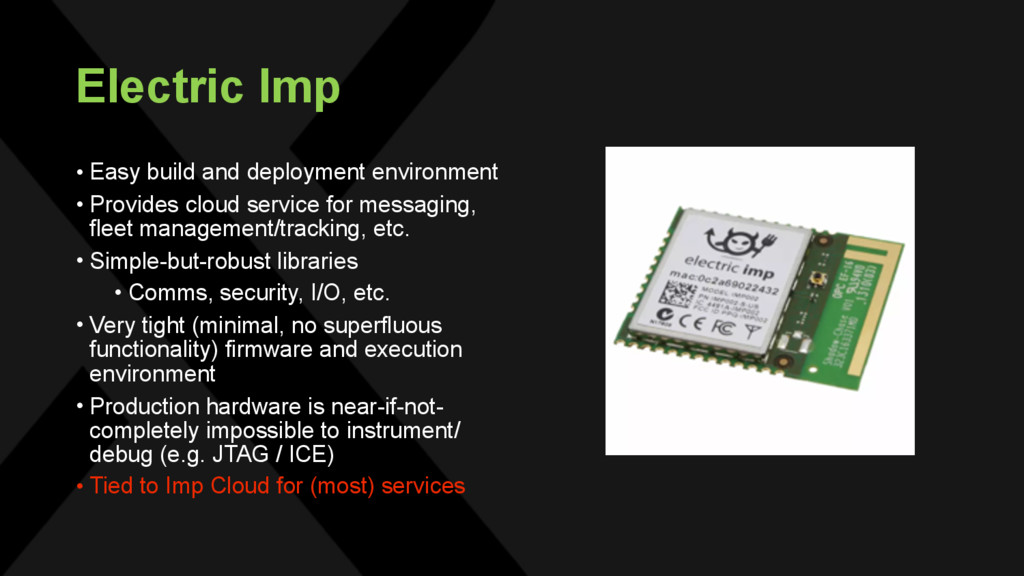
Electric Imp • Easy build and deployment environment • Provides
cloud service for messaging, fleet management/tracking, etc. • Simple-but-robust libraries • Comms, security, I/O, etc. • Very tight (minimal, no superfluous functionality) firmware and execution environment • Production hardware is near-if-not- completely impossible to instrument/ debug (e.g. JTAG / ICE) • Tied to Imp Cloud for (most) services -
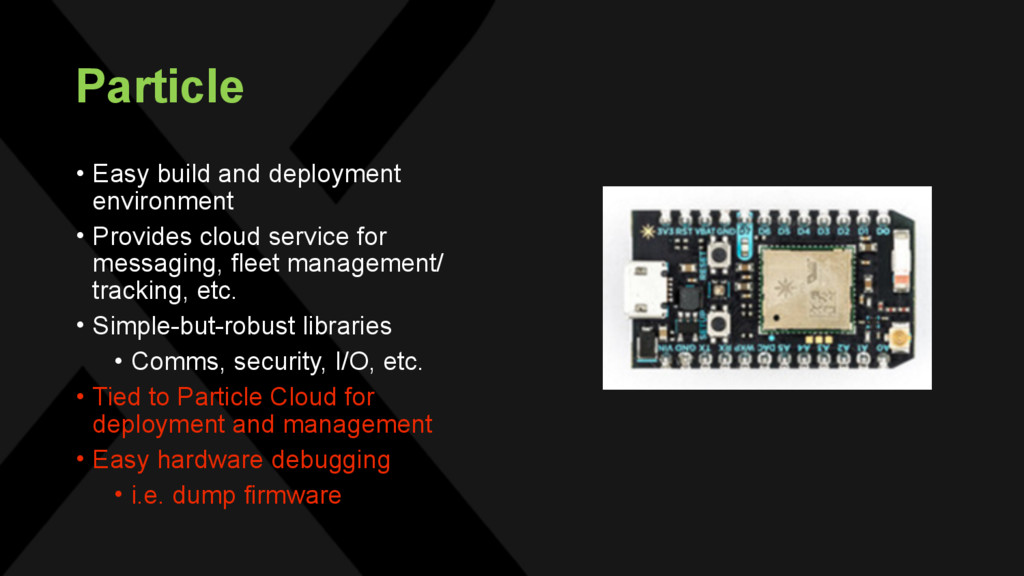
Particle • Easy build and deployment environment • Provides cloud
service for messaging, fleet management/ tracking, etc. • Simple-but-robust libraries • Comms, security, I/O, etc. • Tied to Particle Cloud for deployment and management • Easy hardware debugging • i.e. dump firmware -
Atmel ATSHA204 • Dedicated crypto and key storage • Low
power • Additional physical imposition/ footprint • Increased expense • Additional technical debt • Deprecation • Additional software programming considerations -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms • e.g. 5mA/hr for RSA verification -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms • e.g. 5mA/hr for RSA verification • Innovations in communications to address lack of connectivity -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms • e.g. 5mA/hr for RSA verification • Innovations in communications to address lack of connectivity • Ready-made frameworks for medical/healthcare security -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms • e.g. 5mA/hr for RSA verification • Innovations in communications to address lack of connectivity • Ready-made frameworks for medical/healthcare security • Communications -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms • e.g. 5mA/hr for RSA verification • Innovations in communications to address lack of connectivity • Ready-made frameworks for medical/healthcare security • Communications • Backend services -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms • e.g. 5mA/hr for RSA verification • Innovations in communications to address lack of connectivity • Ready-made frameworks for medical/healthcare security • Communications • Backend services • Auditing / Accounting -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms • e.g. 5mA/hr for RSA verification • Innovations in communications to address lack of connectivity • Ready-made frameworks for medical/healthcare security • Communications • Backend services • Auditing / Accounting • Access Control / AuthZ / AuthC -
Solutions We Would Like To See • On-board crypto co-processors
w/strong algorithms/ciphersuites • Power consumption characterized for standard algorithms • e.g. 5mA/hr for RSA verification • Innovations in communications to address lack of connectivity • Ready-made frameworks for medical/healthcare security • Communications • Backend services • Auditing / Accounting • Access Control / AuthZ / AuthC • etc. -
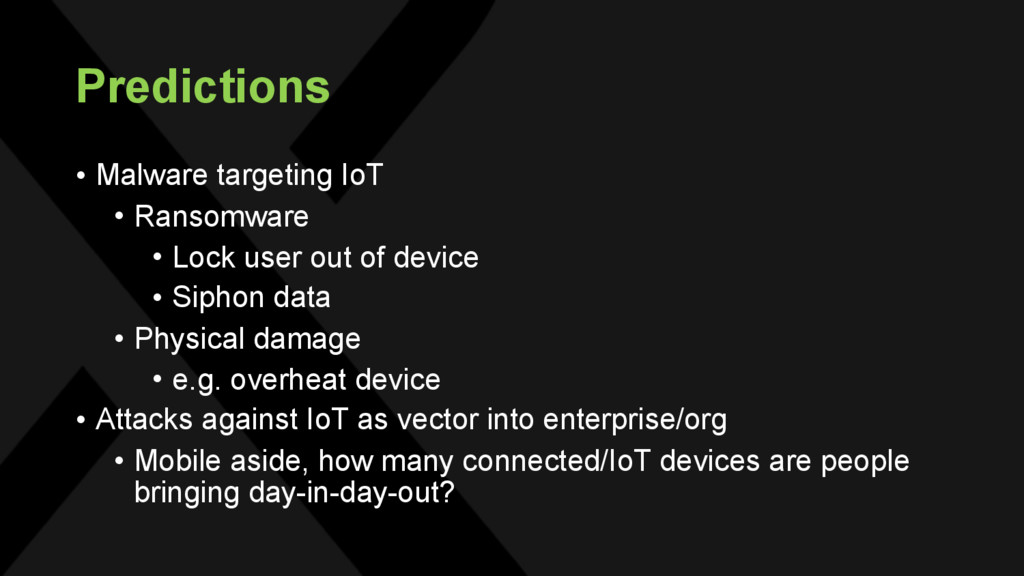
Predictions • Malware targeting IoT • Ransomware • Lock user
out of device • Siphon data -
Predictions • Malware targeting IoT • Ransomware • Lock user
out of device • Siphon data • Physical damage -
Predictions • Malware targeting IoT • Ransomware • Lock user
out of device • Siphon data • Physical damage • e.g. overheat device -
Predictions • Malware targeting IoT • Ransomware • Lock user
out of device • Siphon data • Physical damage • e.g. overheat device • Attacks against IoT as vector into enterprise/org -
Predictions • Malware targeting IoT • Ransomware • Lock user
out of device • Siphon data • Physical damage • e.g. overheat device • Attacks against IoT as vector into enterprise/org • Mobile aside, how many connected/IoT devices are people bringing day-in-day-out?