Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
HTTP Security
Search
RJ Zaworski
September 05, 2014
Technology
210
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
HTTP Security
RJ Zaworski
September 05, 2014
More Decks by RJ Zaworski
See All by RJ Zaworski
Computing Lessons from the Atomic Age: Complexity, Safety, and Ethics
rjz
0
130
Beyond the Single-Page App: React and the Servers that Serve it
rjz
0
110
Typesafe(ish) React
rjz
1
710
Front-end optimization
rjz
1
490
Technical Interviewing
rjz
0
280
Interop! Building a better Backbone.View
rjz
0
120
Front-end optimization
rjz
4
300
Other Decks in Technology
See All in Technology
FactoryBotアンチパターン / factory_bot anti-patterns
toshimaru
0
150
UniFi(ユニファイ)AIカメラの現場活用
ludicmind
1
420
AI時代のPRレビューにどう向き合うか?
kairim0
1
210
hackers_champloo_2026_tidb
makocchi
0
140
Loop Engineering, beyond prompt, context, and harness engineering
glaforge
0
100
Deep Data Security 機能解説
oracle4engineer
PRO
2
800
組み立てて楽しむ AWS Blocks 入門
kmiya84377
0
230
Claude Code本は、どのように執筆チームで書かれたか
oikon48
1
360
分析AIエージェントを育てる、動く環境を育てる
codatum
1
1k
TinyGoでオブザーバビリティ?OpenTelemetryはTinyGoで使えるのか / Is OpenTelemetry available in TinyGo environment?
ymotongpoo
2
140
脆弱性診断って、何をしているの? 〜弱点を見つけて、会社の改善につなげるまで〜
keeg
0
880
Cognition AI Japan - ウェビナー2_テストQA_運用監視
cogakira
0
140
Featured
See All Featured
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
Imperfection Machines: The Place of Print at Facebook
scottboms
270
14k
Claude Code どこまでも/ Claude Code Everywhere
nwiizo
68
59k
[Rails World 2023 - Day 1 Closing Keynote] - The Magic of Rails
eileencodes
38
3.1k
Scaling GitHub
holman
464
140k
Information Architects: The Missing Link in Design Systems
soysaucechin
1
1.2k
Why You Should Never Use an ORM
jnunemaker
PRO
61
10k
For a Future-Friendly Web
brad_frost
184
10k
The Straight Up "How To Draw Better" Workshop
denniskardys
239
140k
The Impact of AI in SEO - AI Overviews June 2024 Edition
aleyda
6
1.2k
We Analyzed 250 Million AI Search Results: Here's What I Found
joshbly
2
2k
Why Our Code Smells
bkeepers
PRO
340
58k
Transcript
HTTP Security A matter of trust rj zaworski, versal inc.
· @rjzaworski · github.com/rjz
Browsers ★ Do what servers tell them to ★ Respect
standards (mostly) ★ Render as much of the server response as they can
Trust is a Big Deal ★ Servers can be compromised,
impersonated, or simply misconfigured ★ How can we tell if content is trustworthy? The short answer is, “we can’t”.
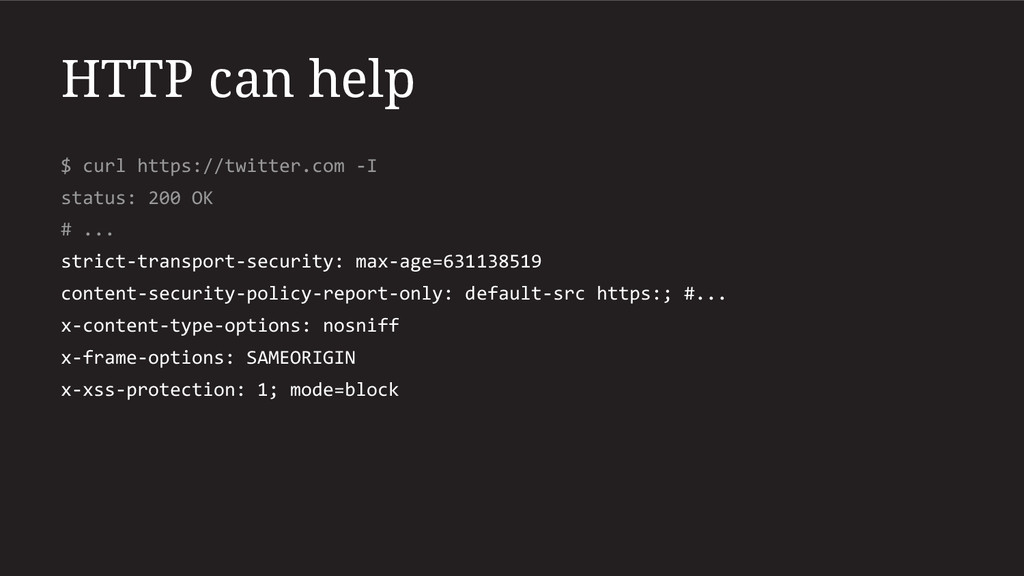
HTTP can help $ curl https://twitter.com -I status: 200 OK
# ... strict-transport-security: max-age=631138519 content-security-policy-report-only: default-src https:; #... x-content-type-options: nosniff x-frame-options: SAMEORIGIN x-xss-protection: 1; mode=block
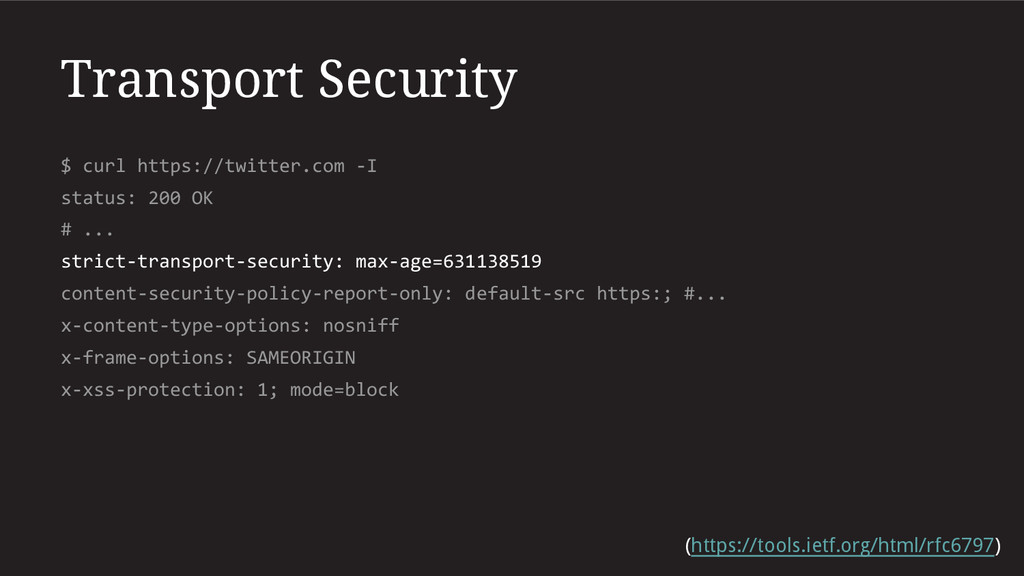
Transport Security $ curl https://twitter.com -I status: 200 OK #
... strict-transport-security: max-age=631138519 content-security-policy-report-only: default-src https:; #... x-content-type-options: nosniff x-frame-options: SAMEORIGIN x-xss-protection: 1; mode=block (https://tools.ietf.org/html/rfc6797)
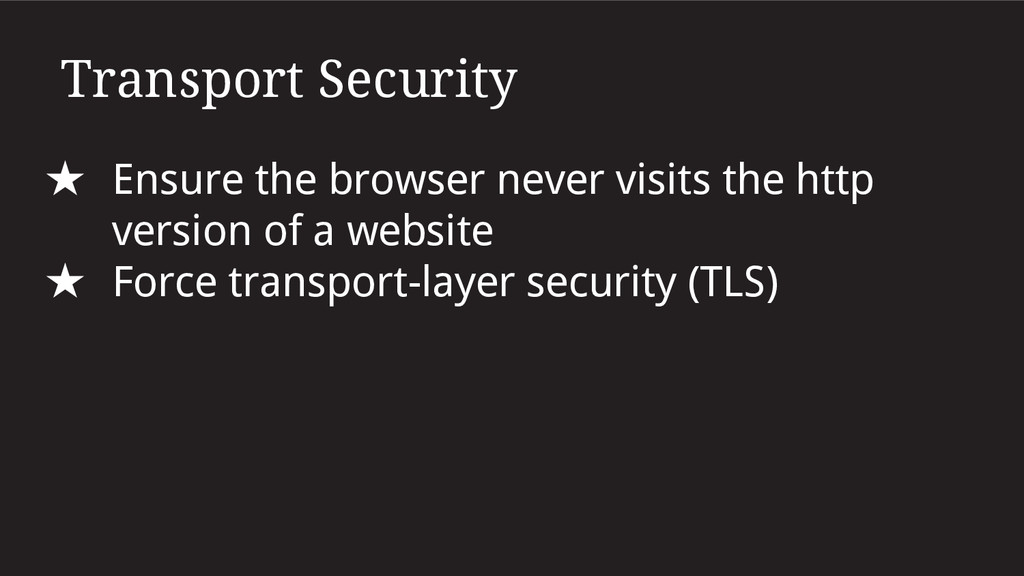
Transport Security ★ Ensure the browser never visits the http
version of a website ★ Force transport-layer security (TLS)
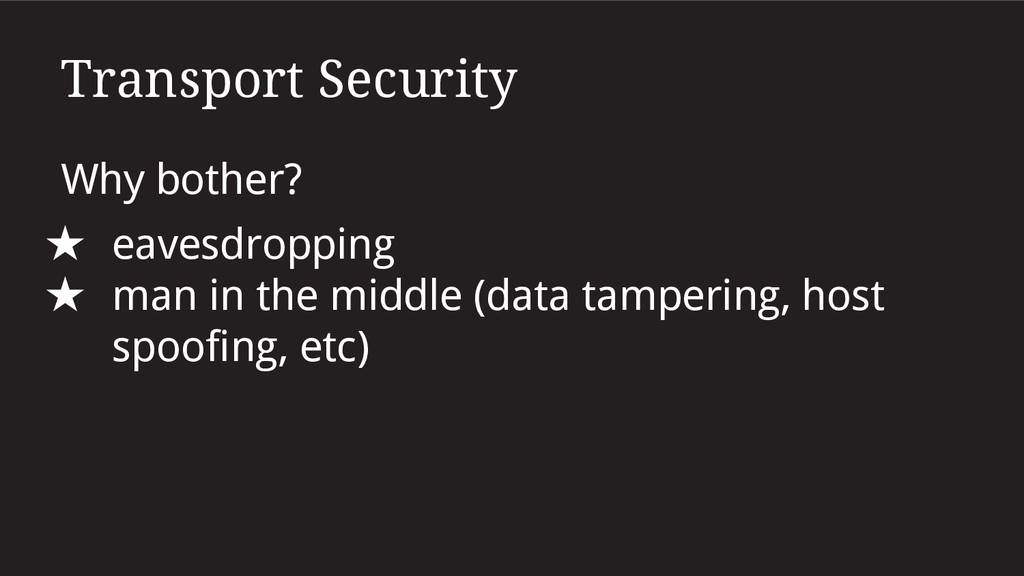
Transport Security Why bother? ★ eavesdropping ★ man in the
middle (data tampering, host spoofing, etc)
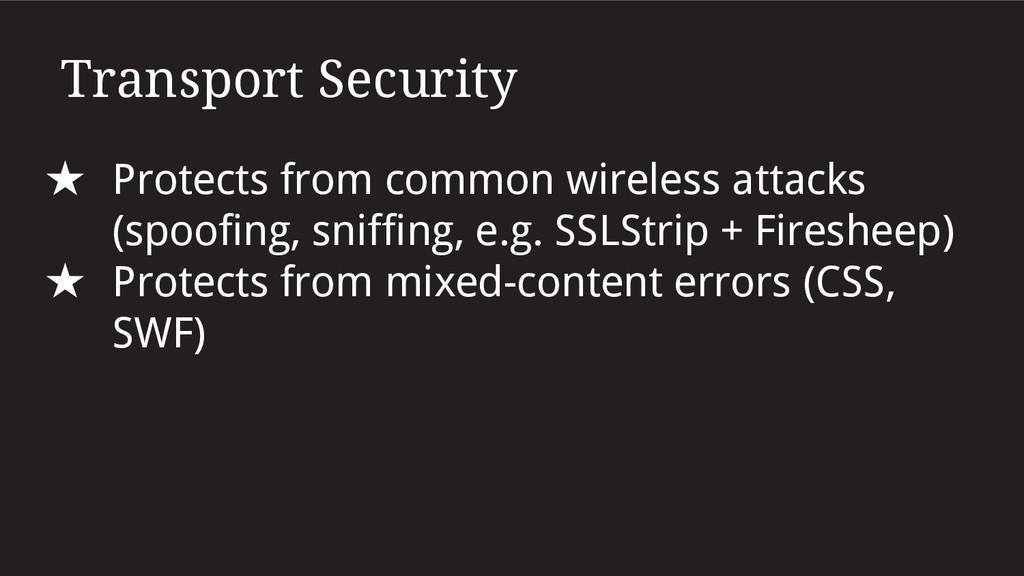
Transport Security ★ Protects from common wireless attacks (spoofing, sniffing,
e.g. SSLStrip + Firesheep) ★ Protects from mixed-content errors (CSS, SWF)
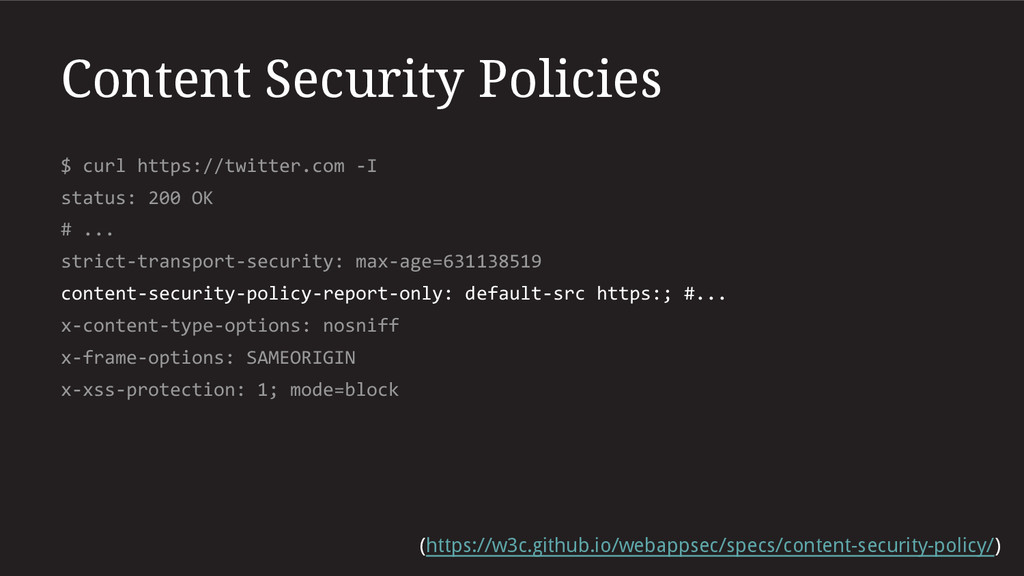
Content Security Policies $ curl https://twitter.com -I status: 200 OK
# ... strict-transport-security: max-age=631138519 content-security-policy-report-only: default-src https:; #... x-content-type-options: nosniff x-frame-options: SAMEORIGIN x-xss-protection: 1; mode=block (https://w3c.github.io/webappsec/specs/content-security-policy/)
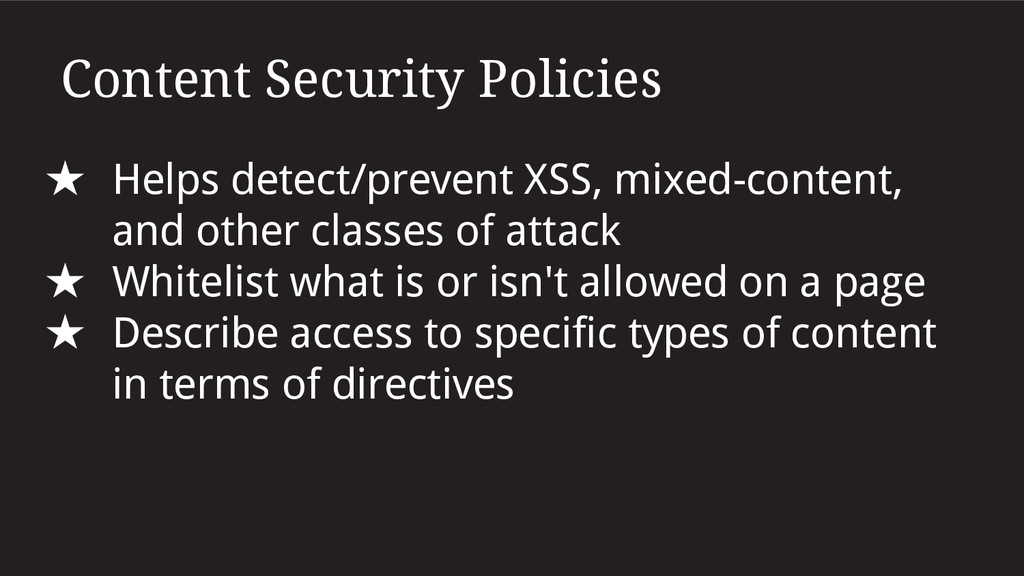
Content Security Policies ★ Helps detect/prevent XSS, mixed-content, and other
classes of attack ★ Whitelist what is or isn't allowed on a page ★ Describe access to specific types of content in terms of directives
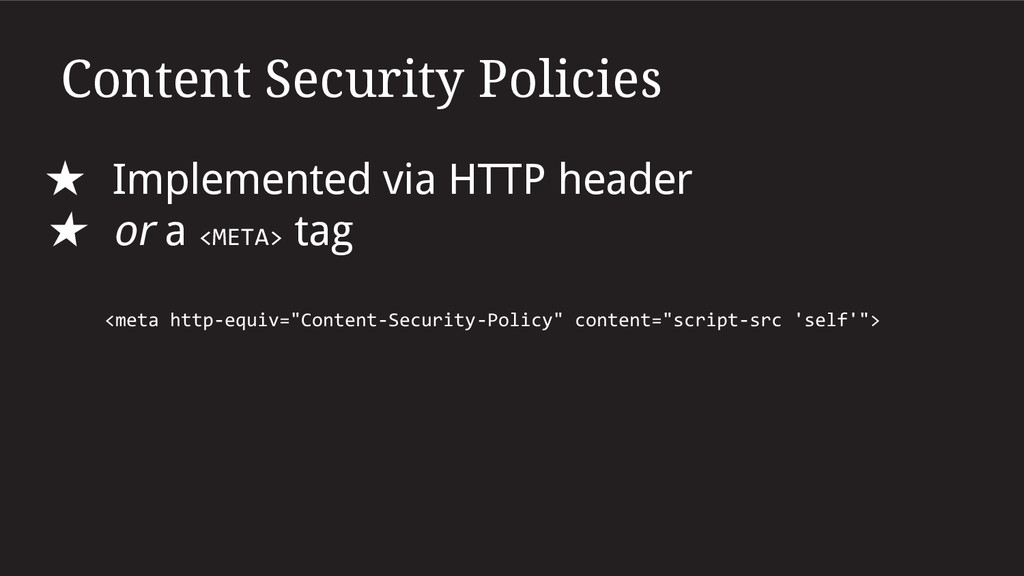
Content Security Policies ★ Implemented via HTTP header ★ or
a <META> tag <meta http-equiv="Content-Security-Policy" content="script-src 'self'">
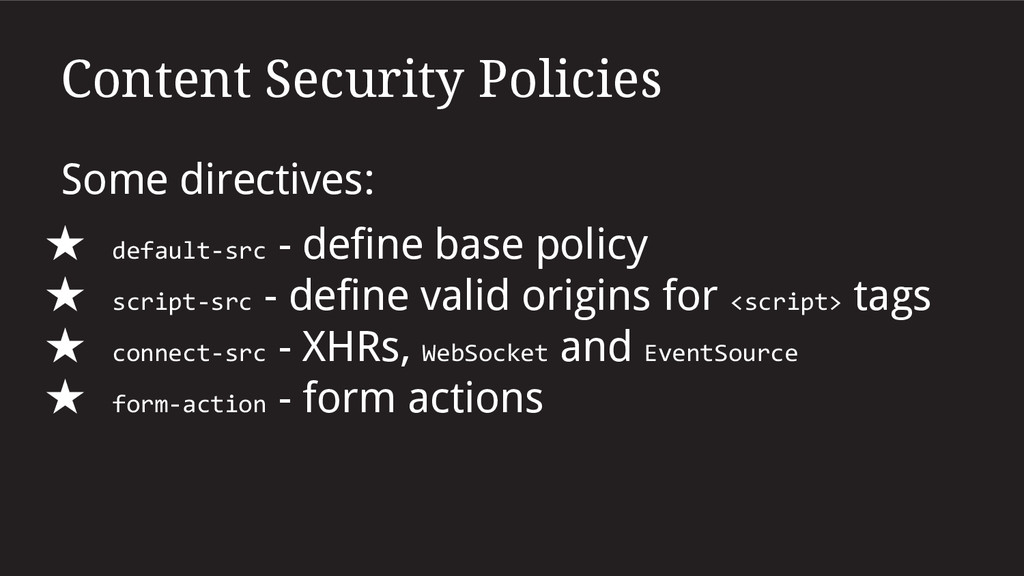
Content Security Policies Some directives: ★ default-src - define base
policy ★ script-src - define valid origins for <script> tags ★ connect-src - XHRs, WebSocket and EventSource ★ form-action - form actions
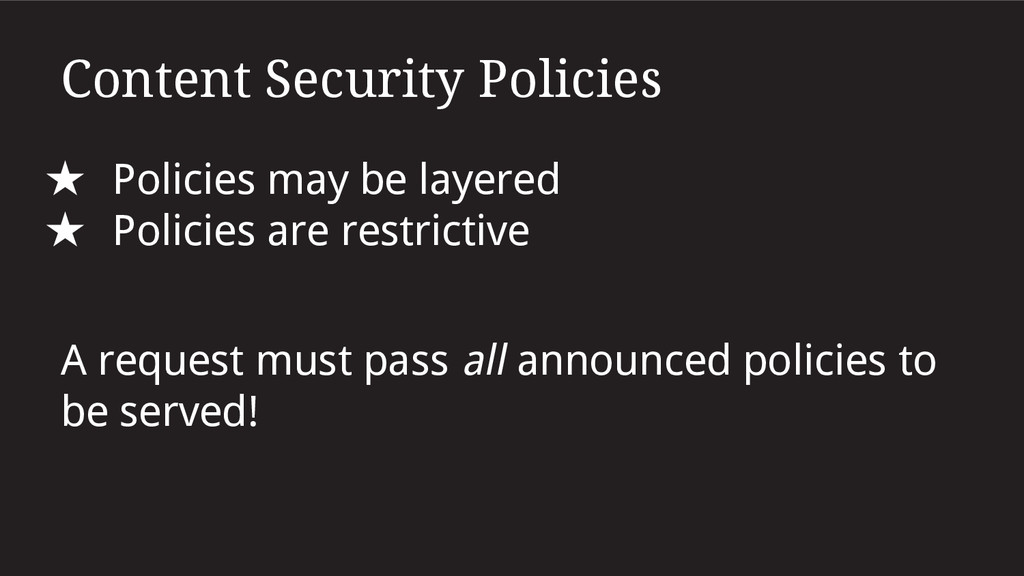
Content Security Policies ★ Policies may be layered ★ Policies
are restrictive A request must pass all announced policies to be served!
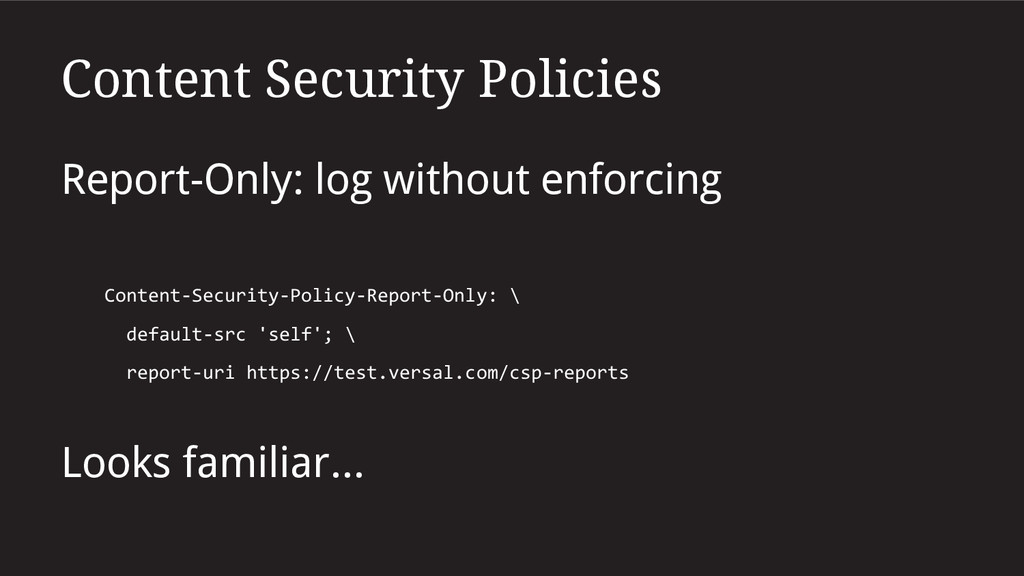
Content Security Policies Report-Only: log without enforcing Content-Security-Policy-Report-Only: \ default-src
'self'; \ report-uri https://test.versal.com/csp-reports Looks familiar...
Content Security Policies Risks: ★ CSS Parsing is still vulnerable
★ Browser support is incomplete
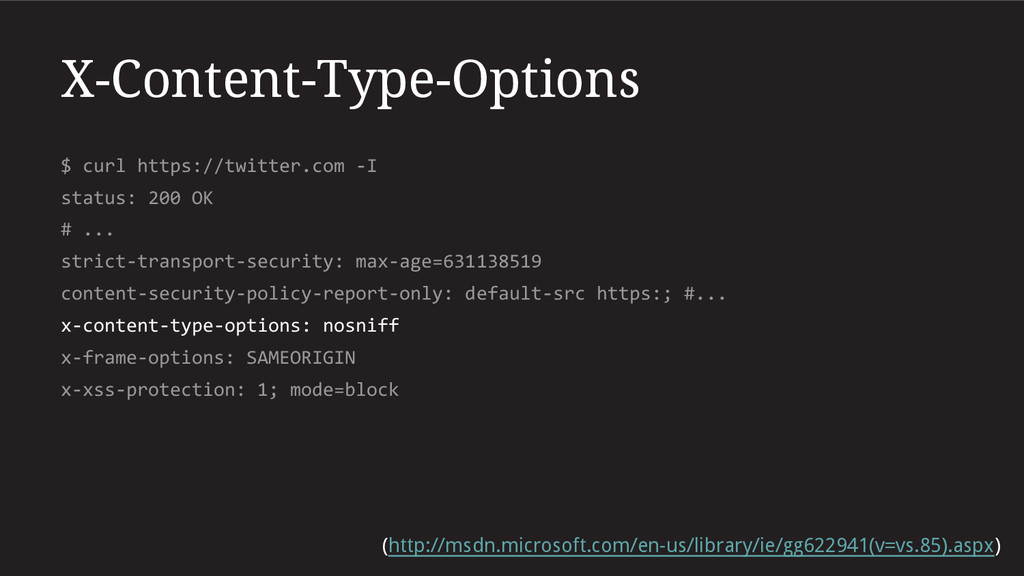
X-Content-Type-Options $ curl https://twitter.com -I status: 200 OK # ...
strict-transport-security: max-age=631138519 content-security-policy-report-only: default-src https:; #... x-content-type-options: nosniff x-frame-options: SAMEORIGIN x-xss-protection: 1; mode=block (http://msdn.microsoft.com/en-us/library/ie/gg622941(v=vs.85).aspx)
X-Content-Type-Options ★ <SCRIPT> and <STYLE> reject responses with incorrect content-types
★ Prevent MIME confusion ★ Implemented in Chrome, IE
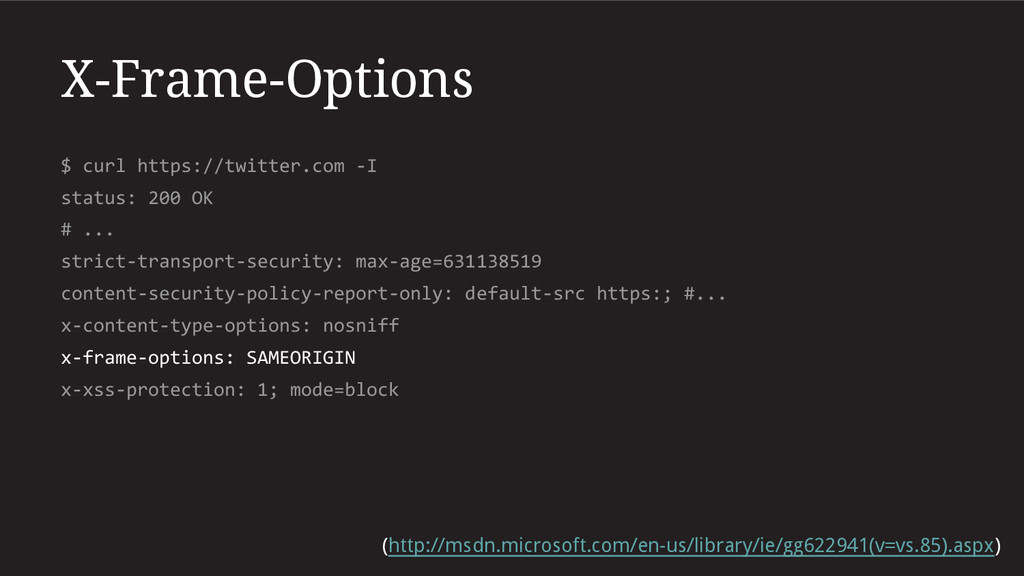
X-Frame-Options $ curl https://twitter.com -I status: 200 OK # ...
strict-transport-security: max-age=631138519 content-security-policy-report-only: default-src https:; #... x-content-type-options: nosniff x-frame-options: SAMEORIGIN x-xss-protection: 1; mode=block (http://msdn.microsoft.com/en-us/library/ie/gg622941(v=vs.85).aspx)
X-Frame-Options ★ Prevents content from being framed ★ Protects from
external clickjacking ★ Three choices: DENY , SAMEORIGIN , or ALLOW-FROM
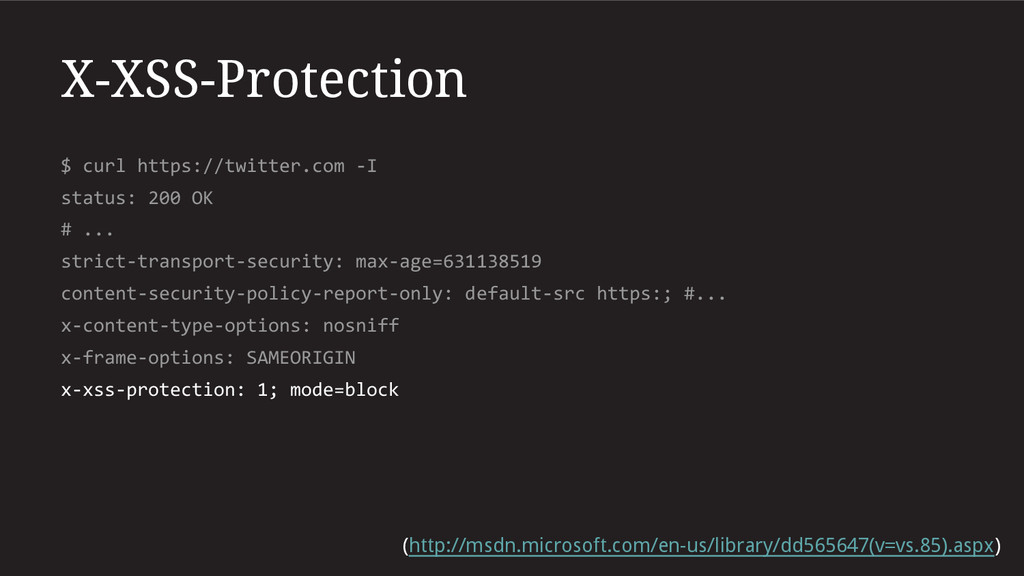
X-XSS-Protection $ curl https://twitter.com -I status: 200 OK # ...
strict-transport-security: max-age=631138519 content-security-policy-report-only: default-src https:; #... x-content-type-options: nosniff x-frame-options: SAMEORIGIN x-xss-protection: 1; mode=block (http://msdn.microsoft.com/en-us/library/dd565647(v=vs.85).aspx)
X-XSS-Protection ★ Browser’s best guess about blocking XSS attempts ★
On by default in Chrome, IE
Further Reading On OWASP: ★ List of Useful Headers ★
HTTP Strict Transport Security ★ Content Security Policy
Thank you! rj zaworski · @rjzaworski · github.com/rjz


 rjz
 toshimaru
 ludicmind
 kairim0
 makocchi
 glaforge
 oracle4engineer
 kmiya84377
 oikon48
 codatum
 ymotongpoo
 keeg
 cogakira
 caitiem20
 scottboms
 nwiizo
 eileencodes
 holman
 soysaucechin
 jnunemaker
 brad_frost
 denniskardys
 aleyda
 joshbly
 bkeepers