Share
Embed
High Assurance Secure Software Development on the Server Side
Charles Hubain (LINE Plus / Security R&D Team / Senior Security Engineer)
Jonas Lejeune (LINE / Security R&D Team / Senior Security Engineer)
https://tech-verse.me/ja/sessions/70
https://tech-verse.me/en/sessions/70
https://tech-verse.me/ko/sessions/70
Tech-Verse2022
November 17, 2022
Transcript
146 slides
-
Agenda 1. Background 2. Security Architecture 3. Hardware Security Module
4. Intel® Software Guard Extensions 5. Practical Considerations -
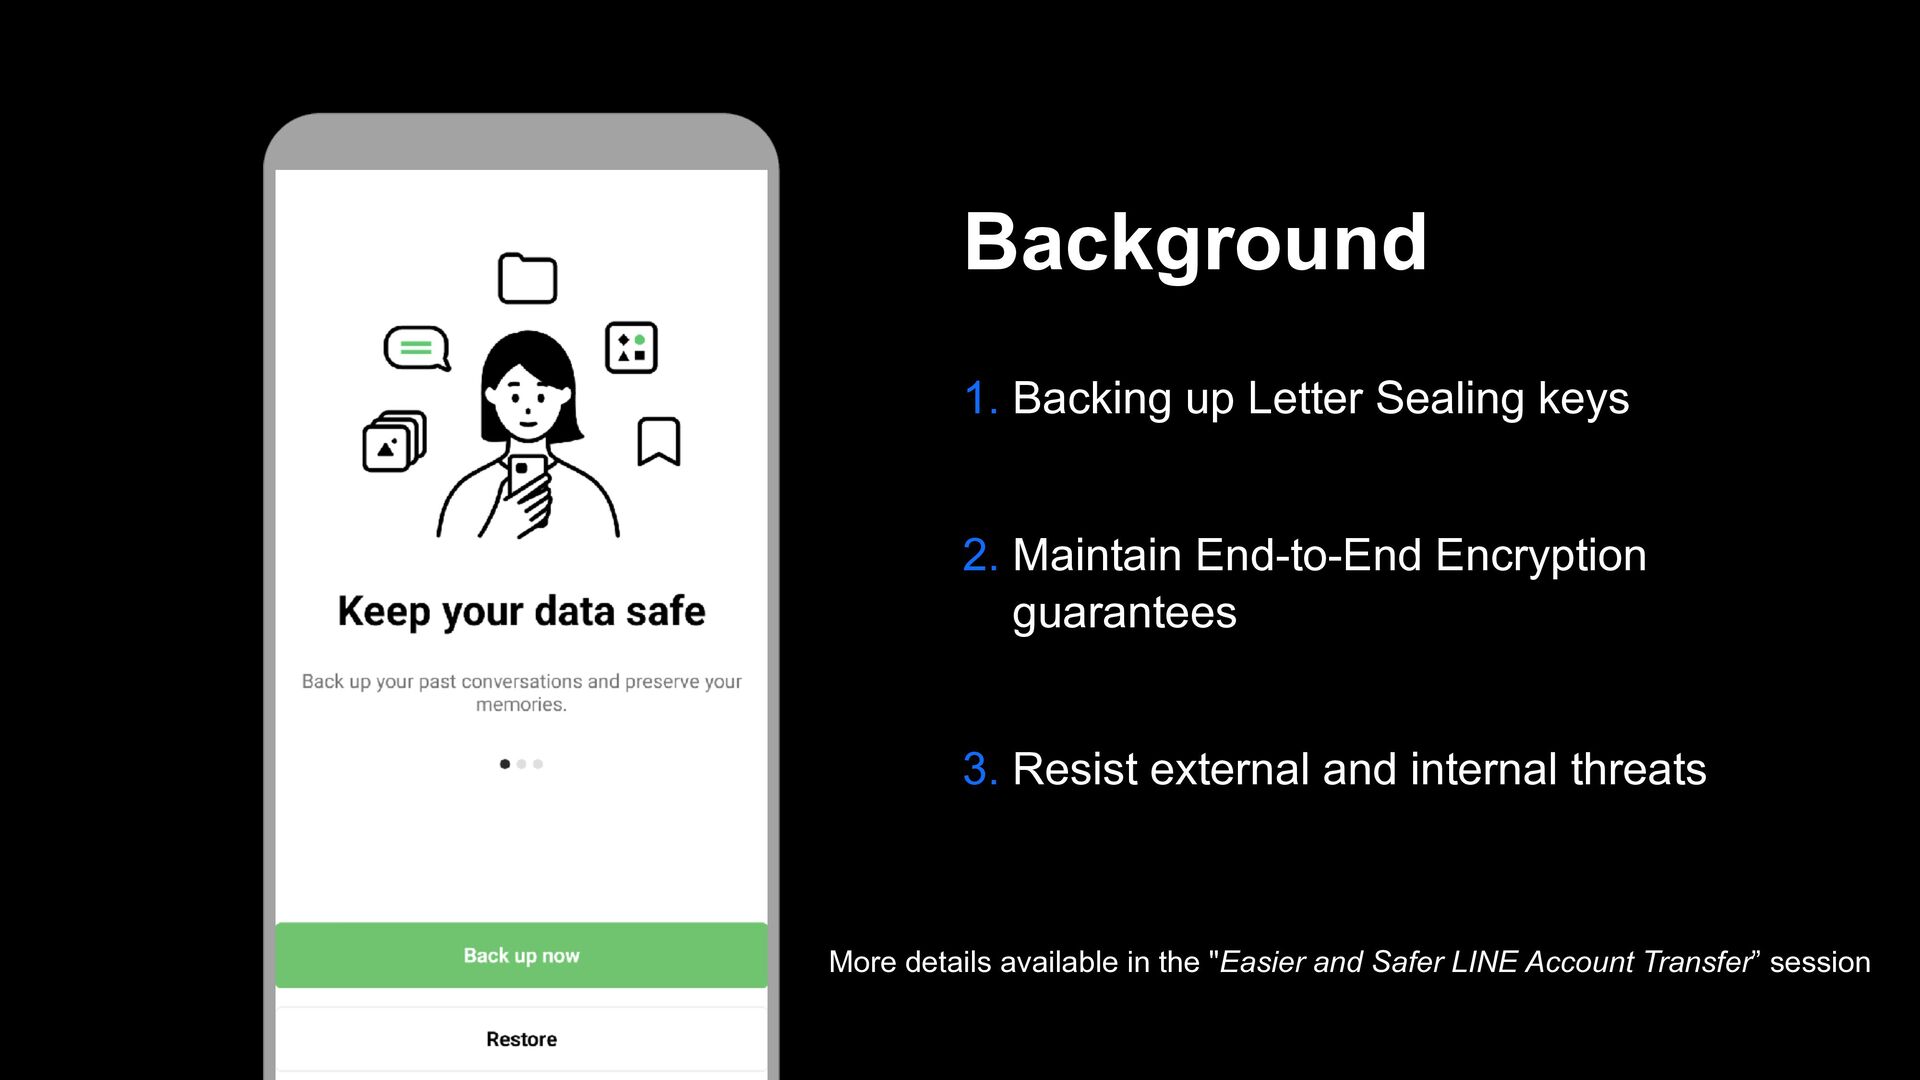
1. Backing up Letter Sealing keys 2. Maintain End-to-End Encryption
guarantees 3. Resist external and internal threats Background More details available in the "Easier and Safer LINE Account Transfer” session -
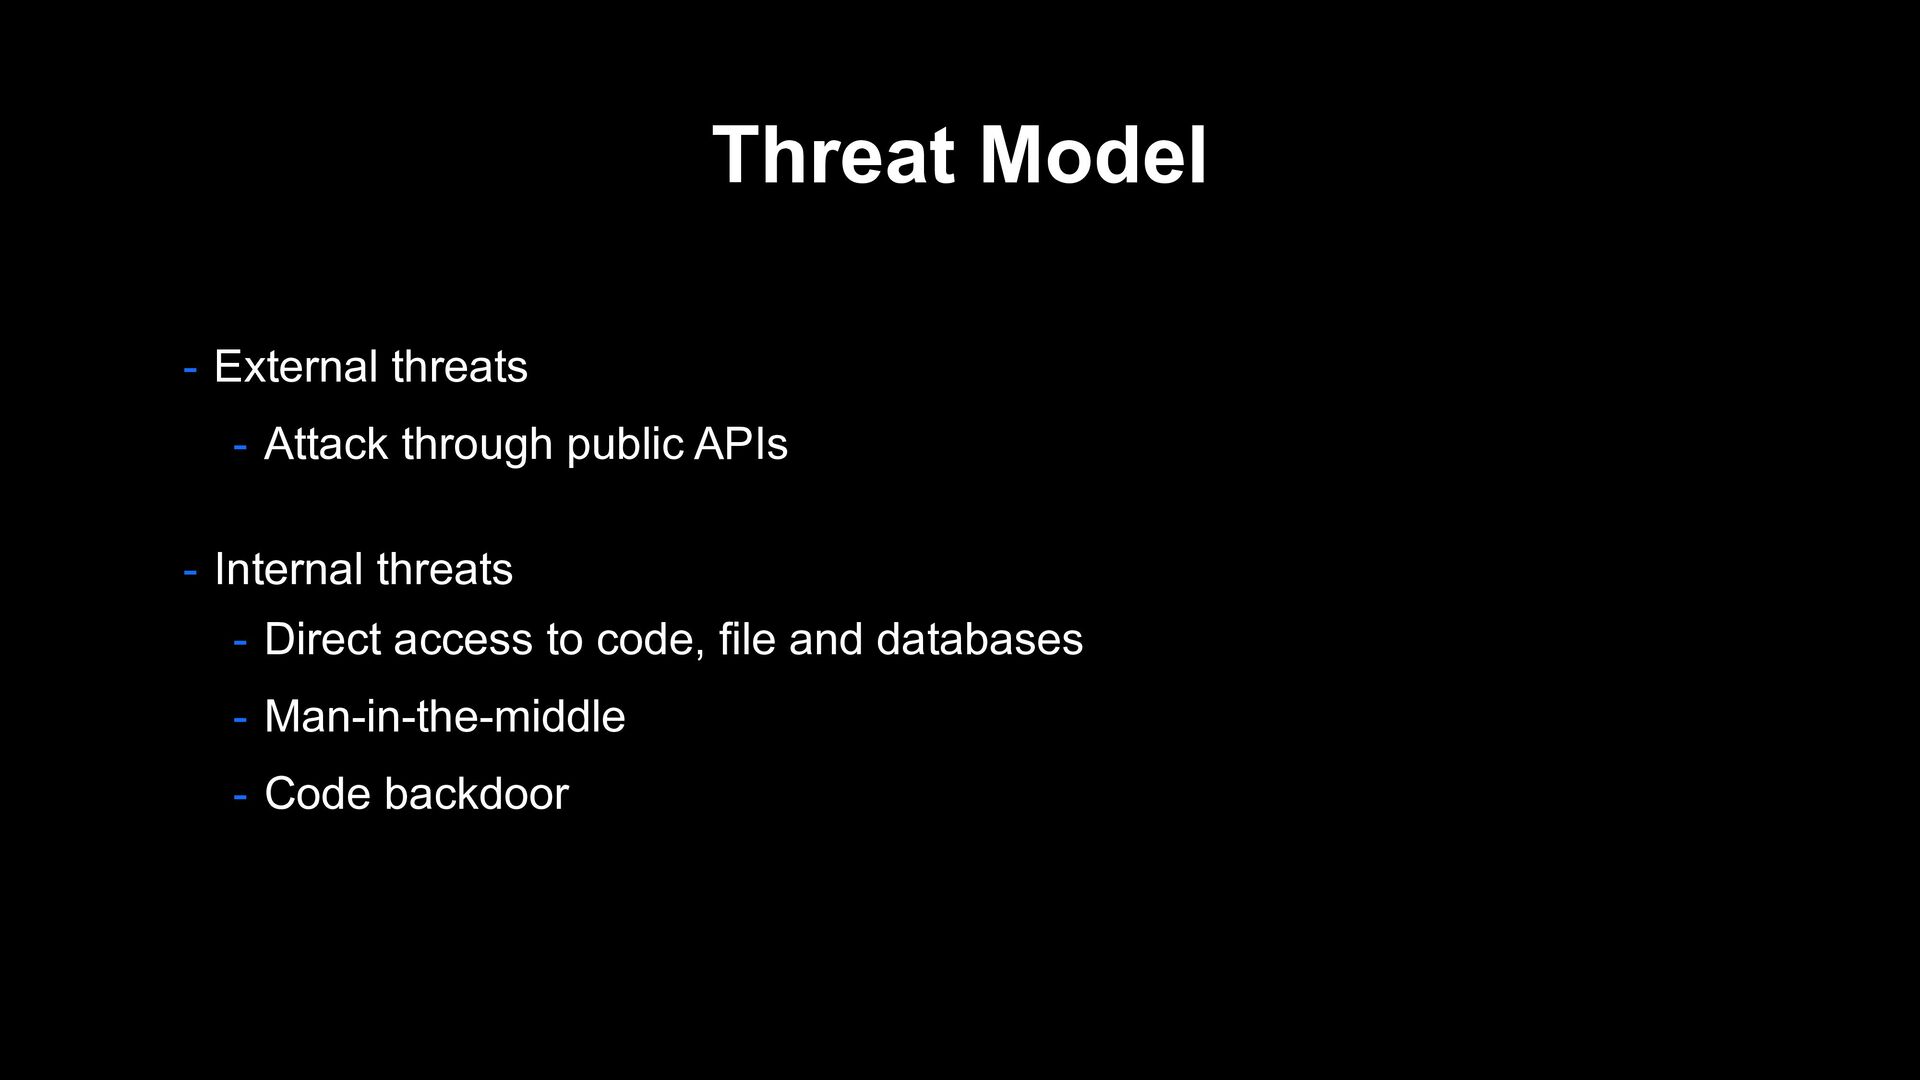
Threat Model - Direct access to code, file and databases
- Man-in-the-middle - Code backdoor - External threats - Attack through public APIs - Internal threats -
Backup of Letter Sealing keys ✳ LINE Developer Day 2019:
Seamless device migration using LINE secure backups LINE Client -
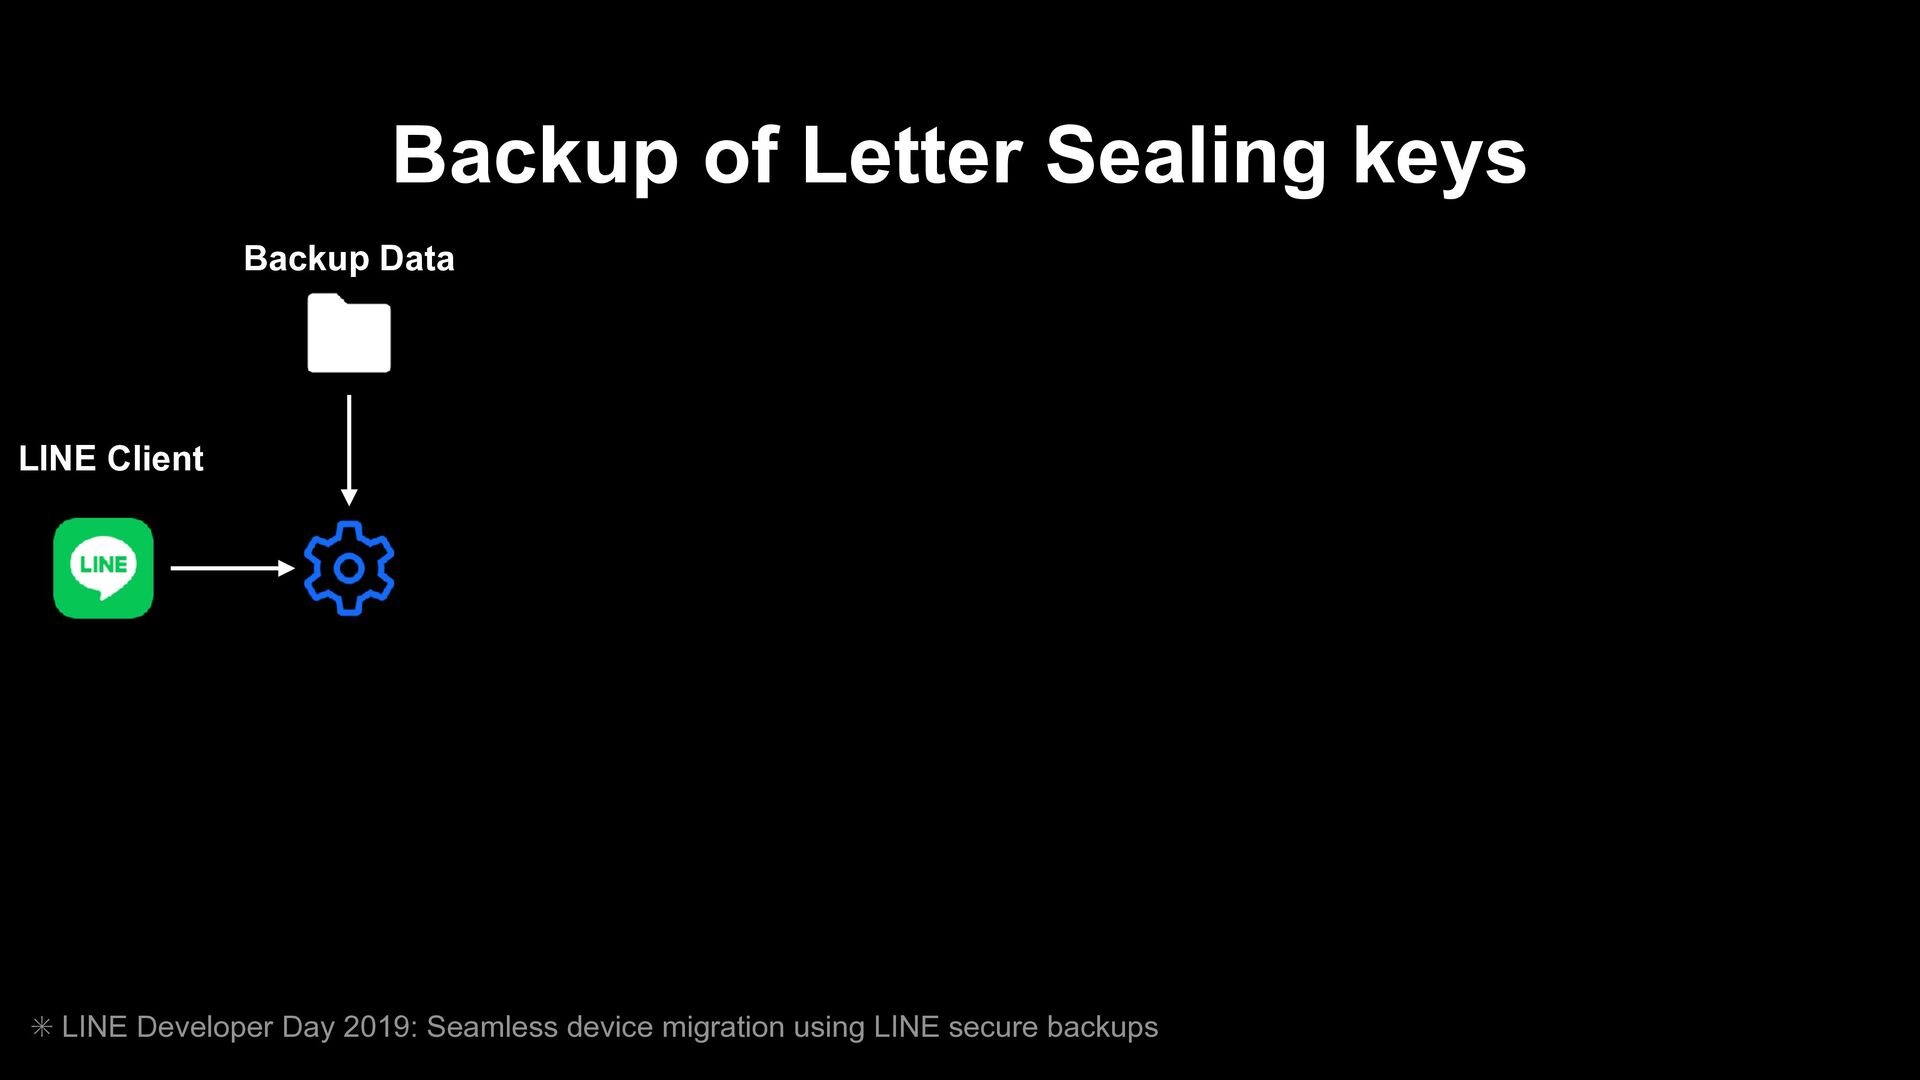
Backup of Letter Sealing keys ✳ LINE Developer Day 2019:
Seamless device migration using LINE secure backups LINE Client Backup Data -
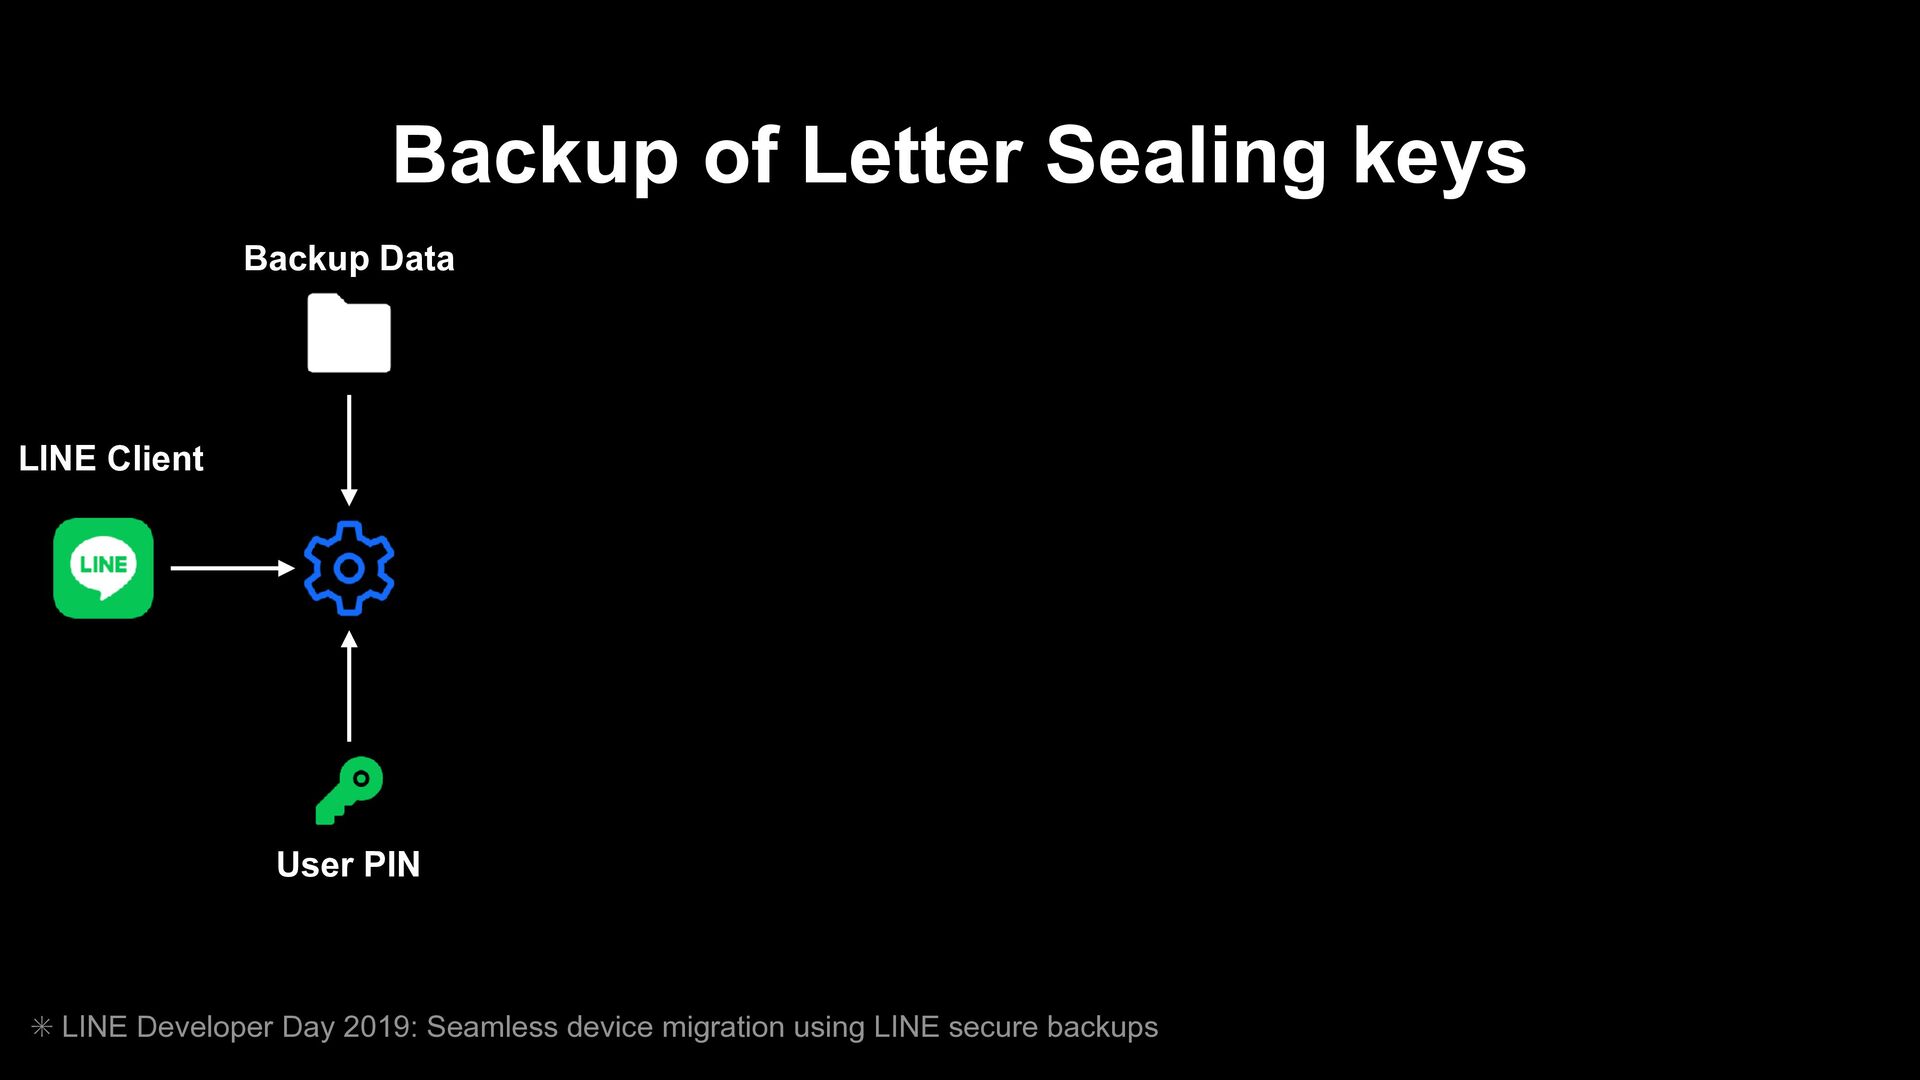
Backup of Letter Sealing keys ✳ LINE Developer Day 2019:
Seamless device migration using LINE secure backups LINE Client User PIN Backup Data -
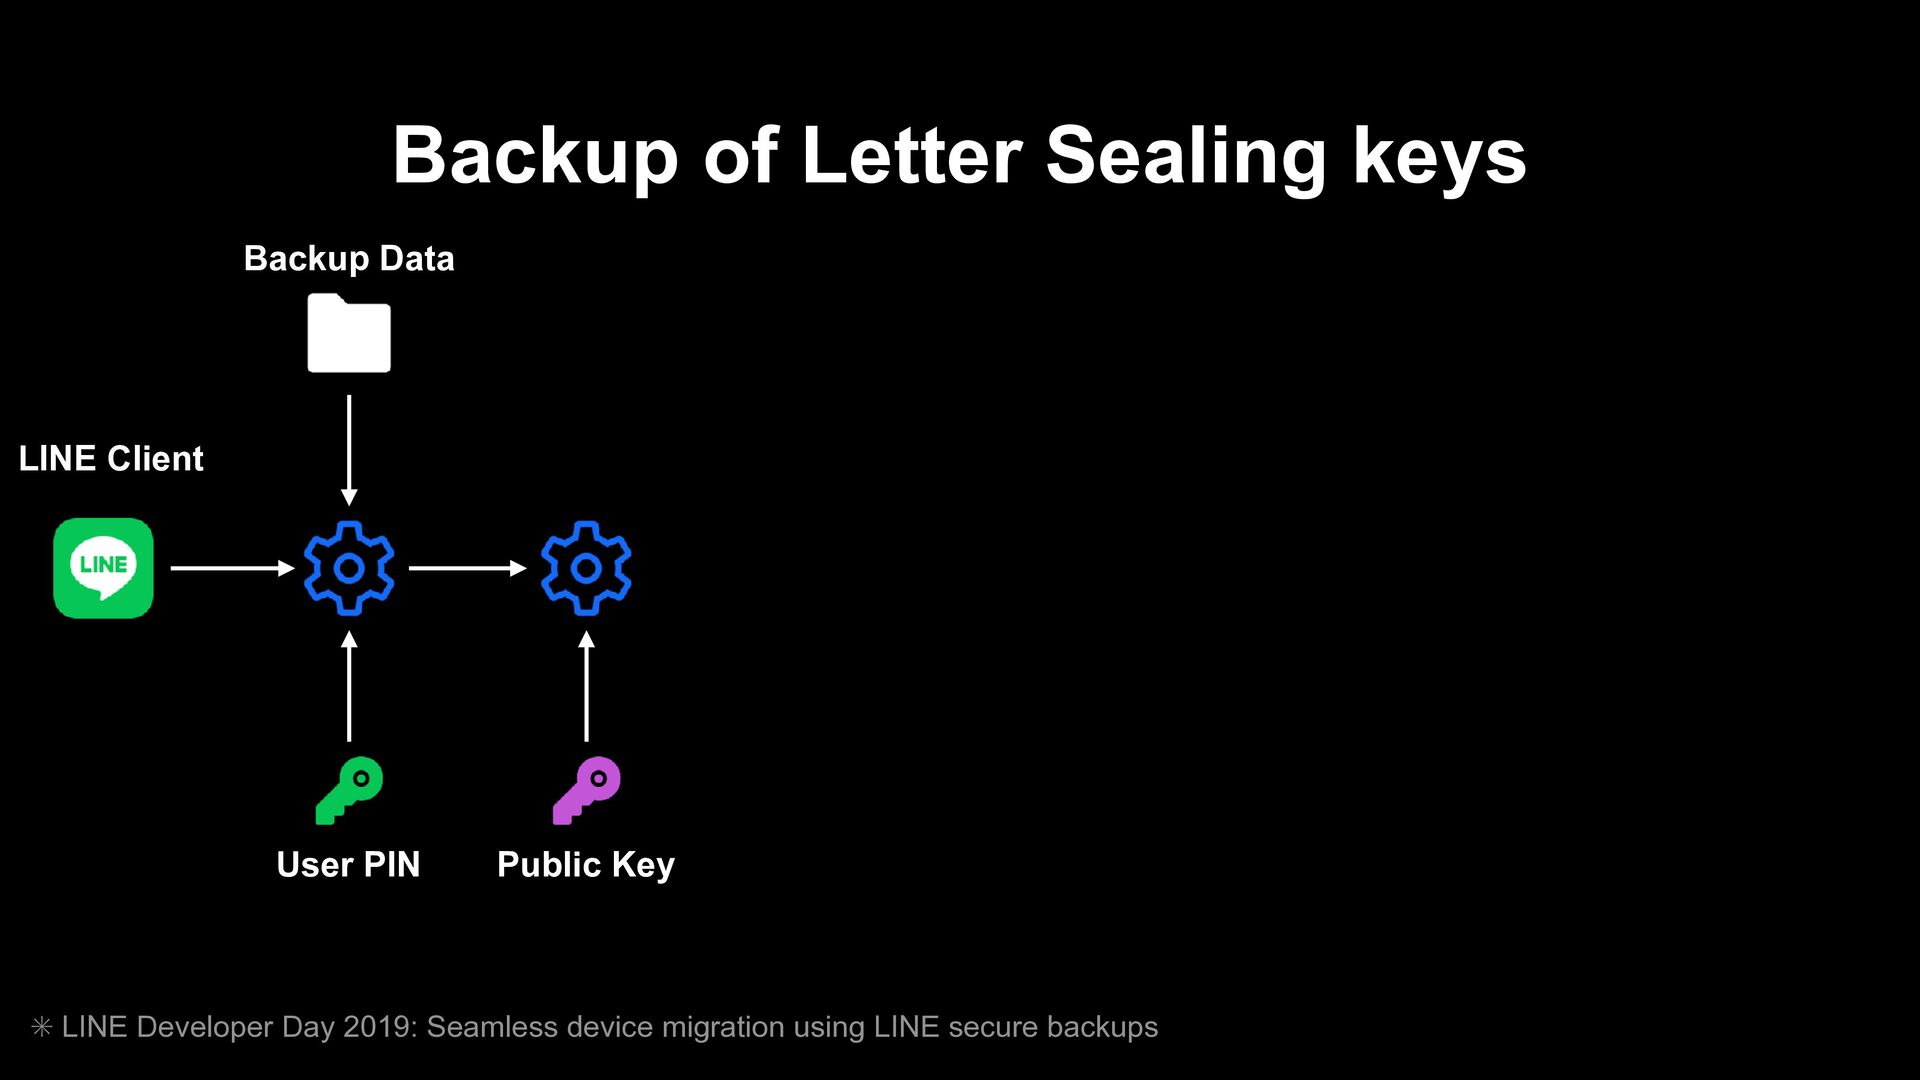
Backup of Letter Sealing keys ✳ LINE Developer Day 2019:
Seamless device migration using LINE secure backups LINE Client User PIN Public Key Backup Data -
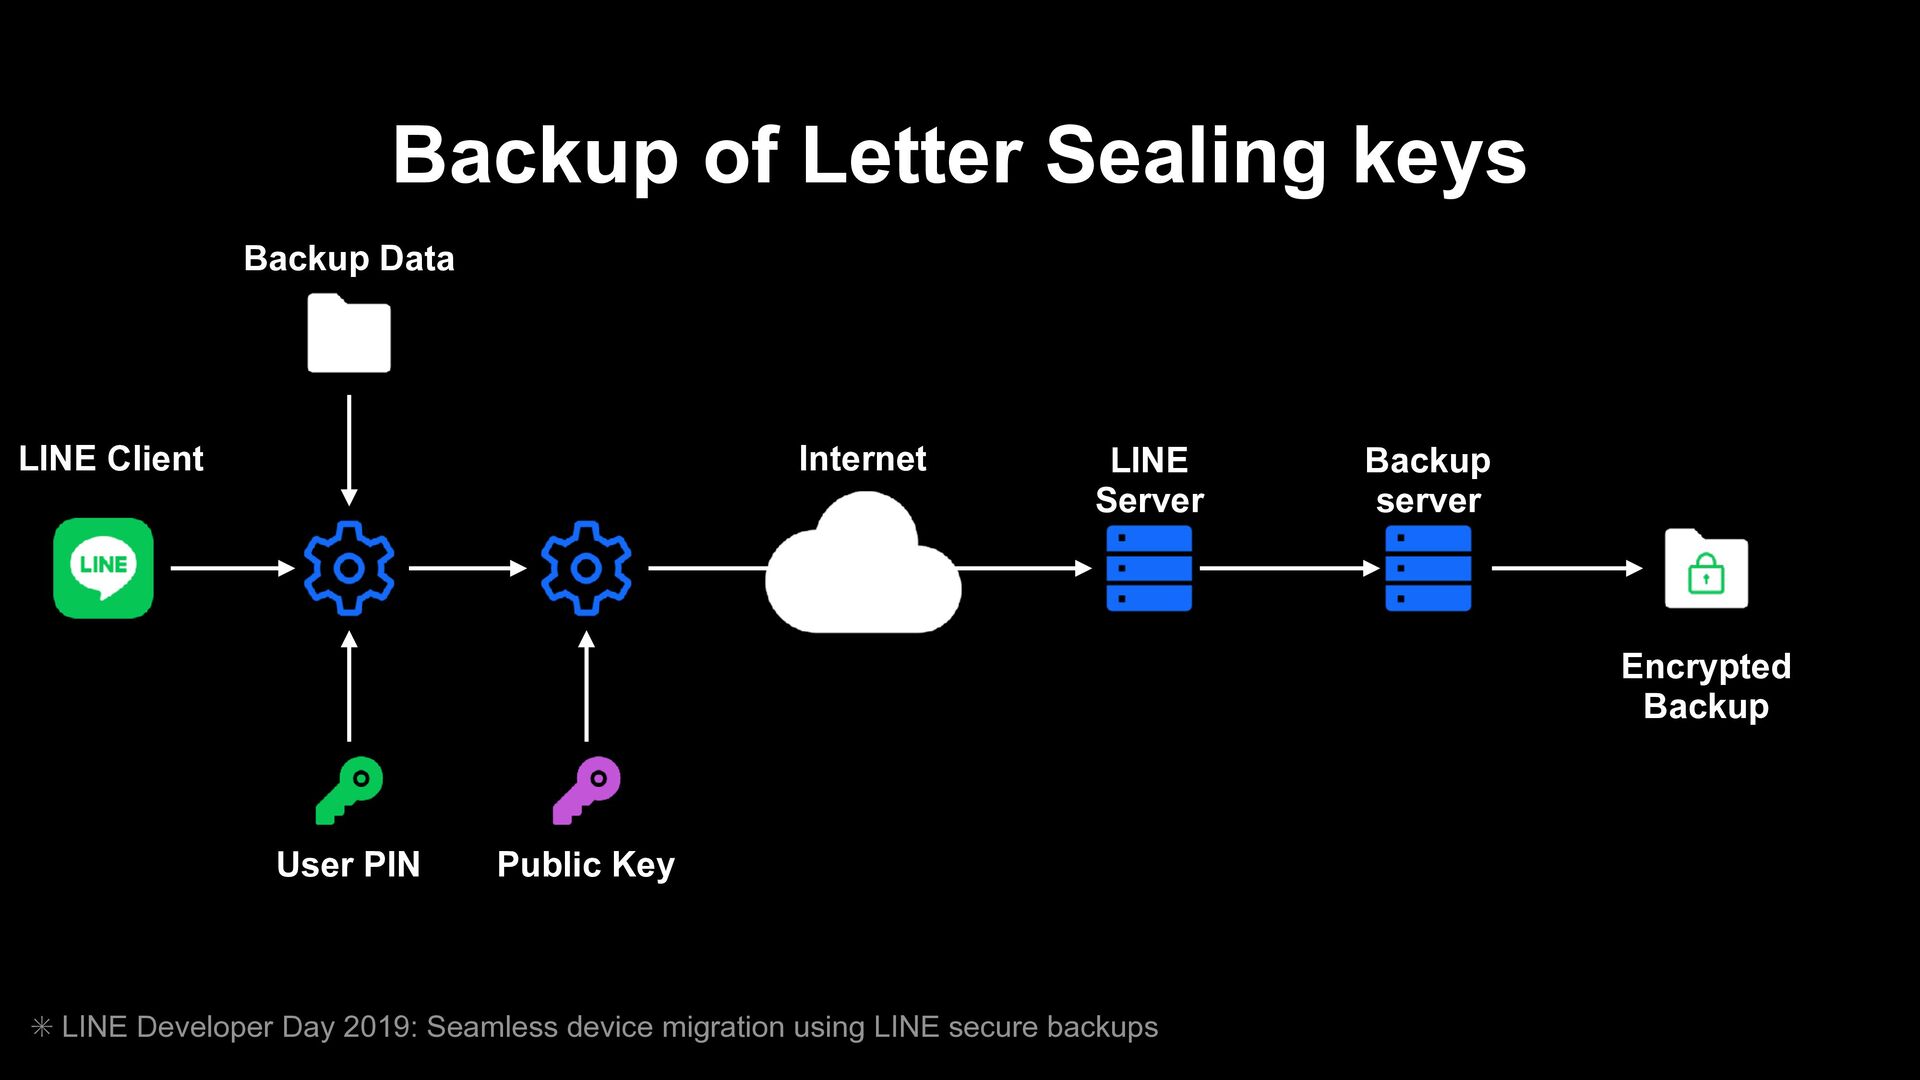
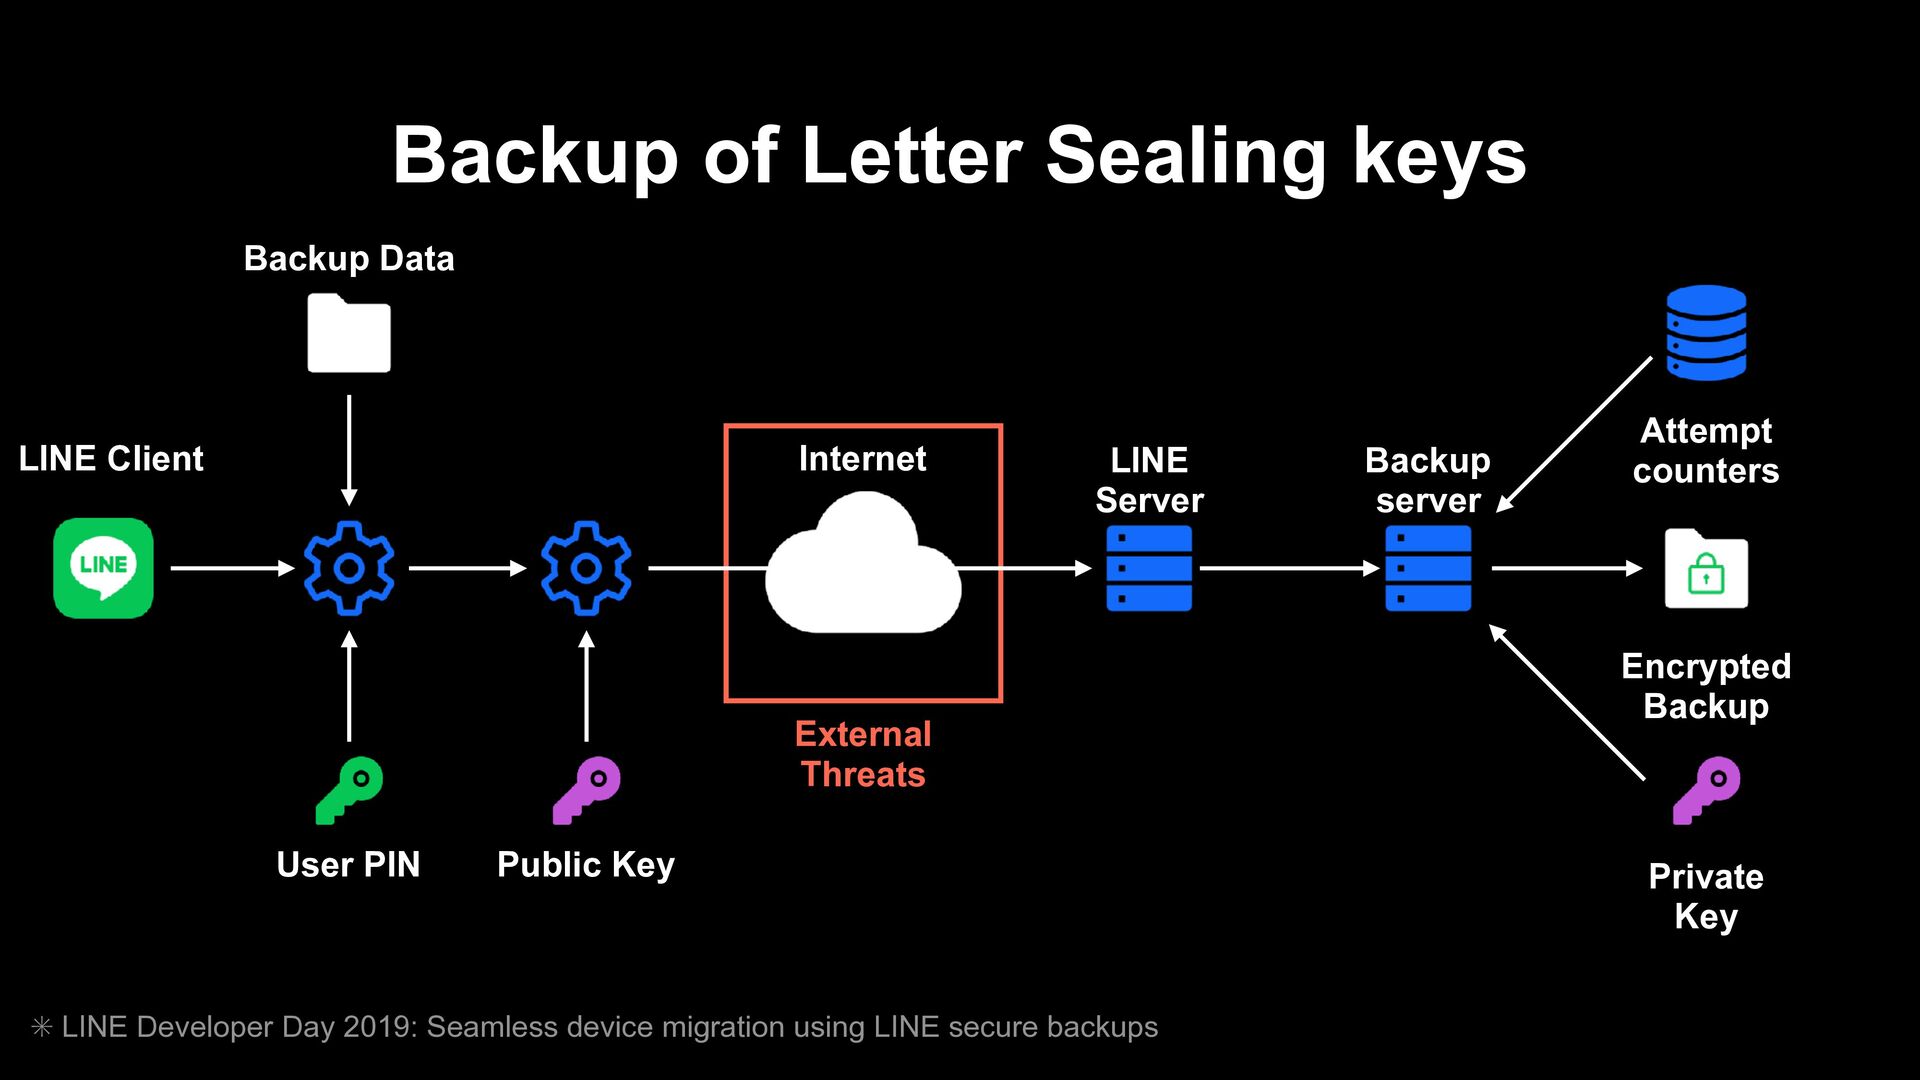
Backup of Letter Sealing keys ✳ LINE Developer Day 2019:
Seamless device migration using LINE secure backups LINE Client LINE Server Backup server Encrypted Backup Internet User PIN Public Key Backup Data -
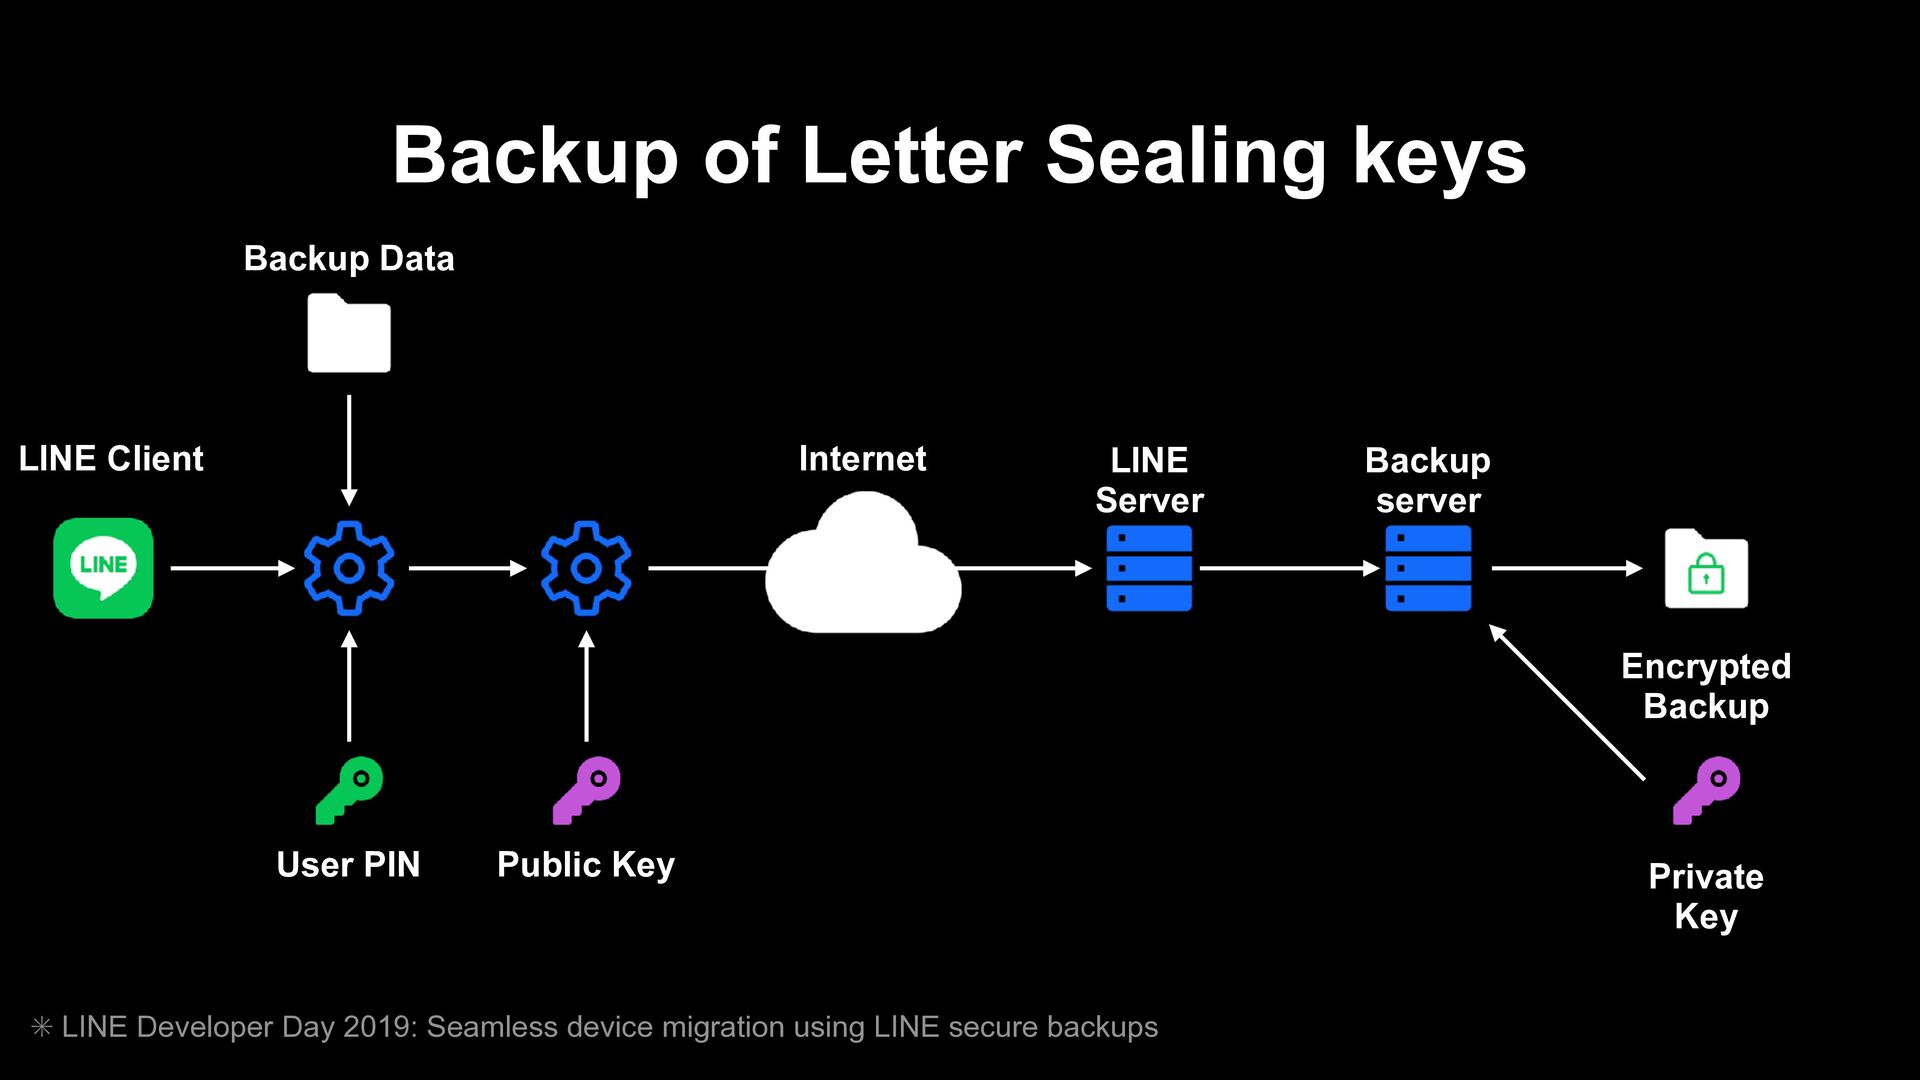
Backup of Letter Sealing keys ✳ LINE Developer Day 2019:
Seamless device migration using LINE secure backups LINE Client LINE Server Backup server Encrypted Backup Internet User PIN Public Key Private Key Backup Data -
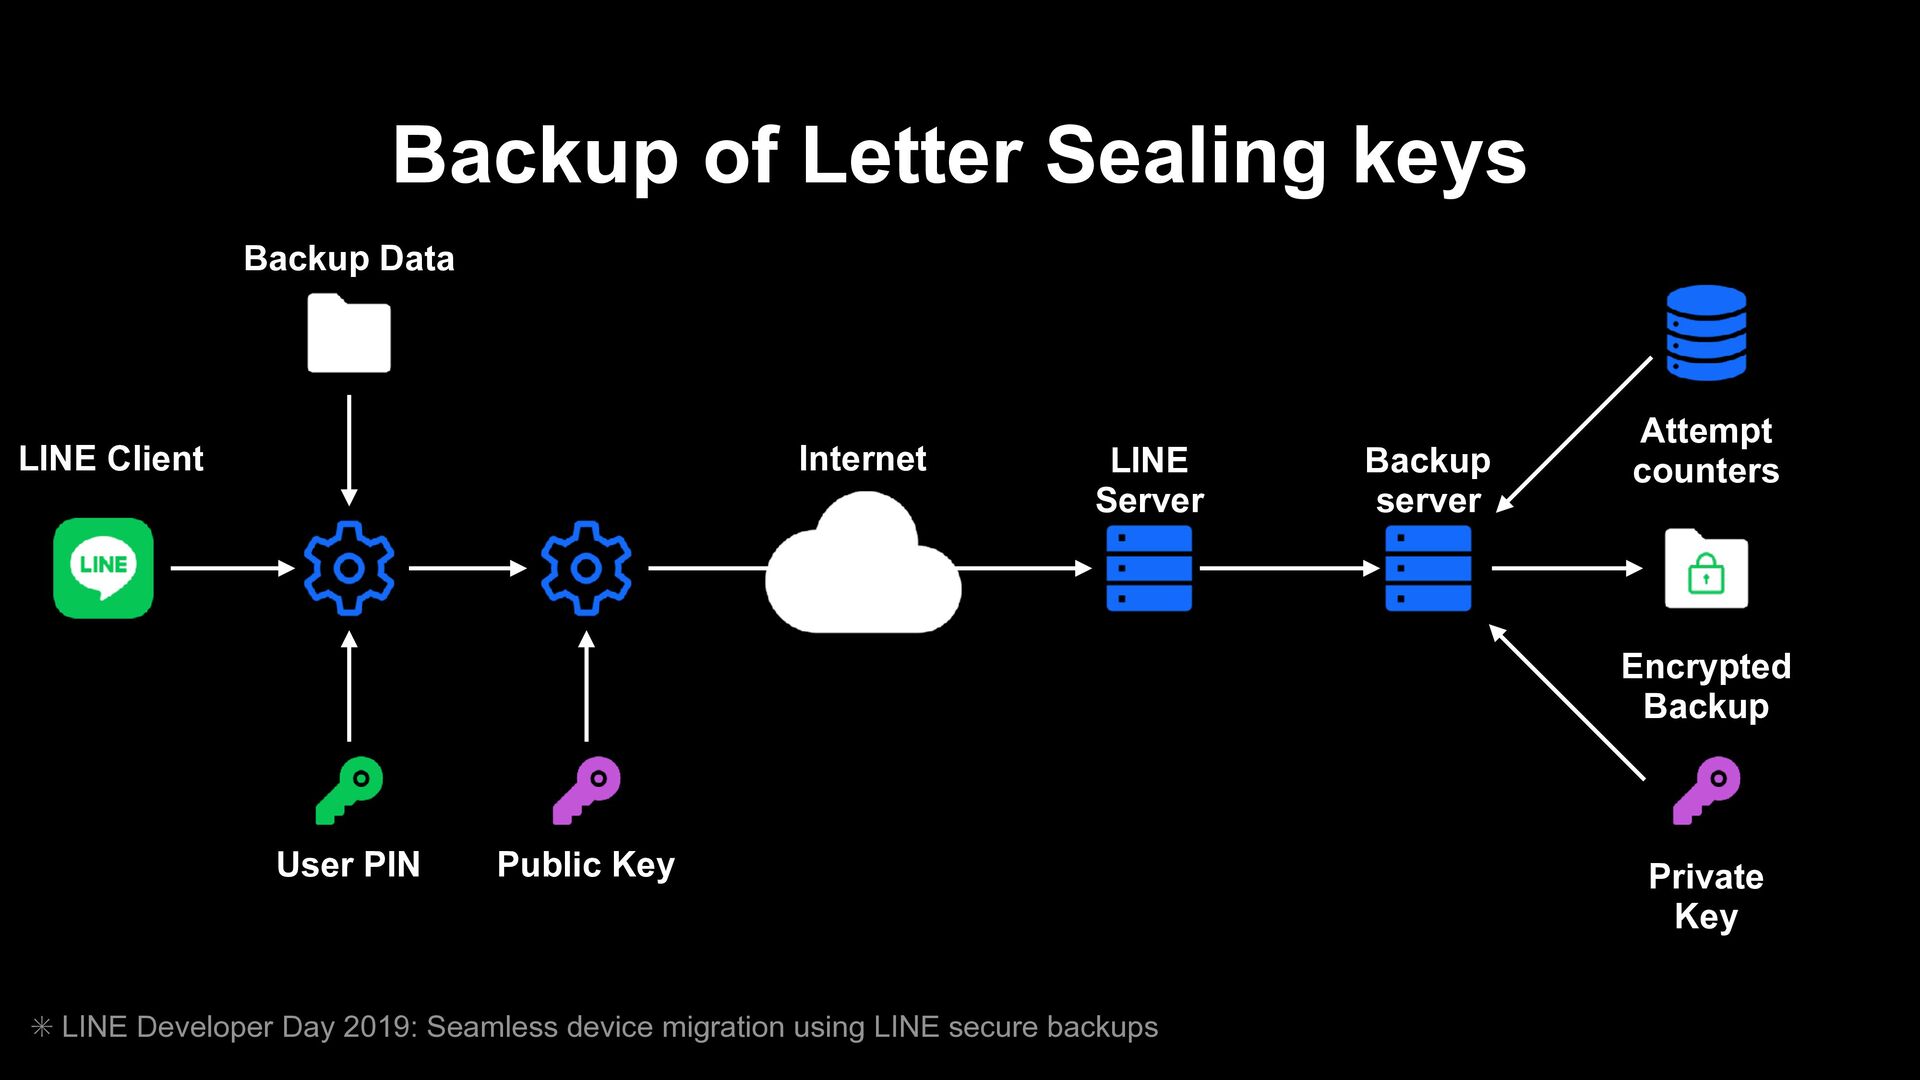
Backup of Letter Sealing keys ✳ LINE Developer Day 2019:
Seamless device migration using LINE secure backups LINE Client LINE Server Backup server Encrypted Backup Internet User PIN Public Key Private Key Attempt counters Backup Data -
External Threats Backup of Letter Sealing keys ✳ LINE Developer
Day 2019: Seamless device migration using LINE secure backups LINE Client LINE Server Backup server Encrypted Backup Internet User PIN Public Key Private Key Attempt counters Backup Data -
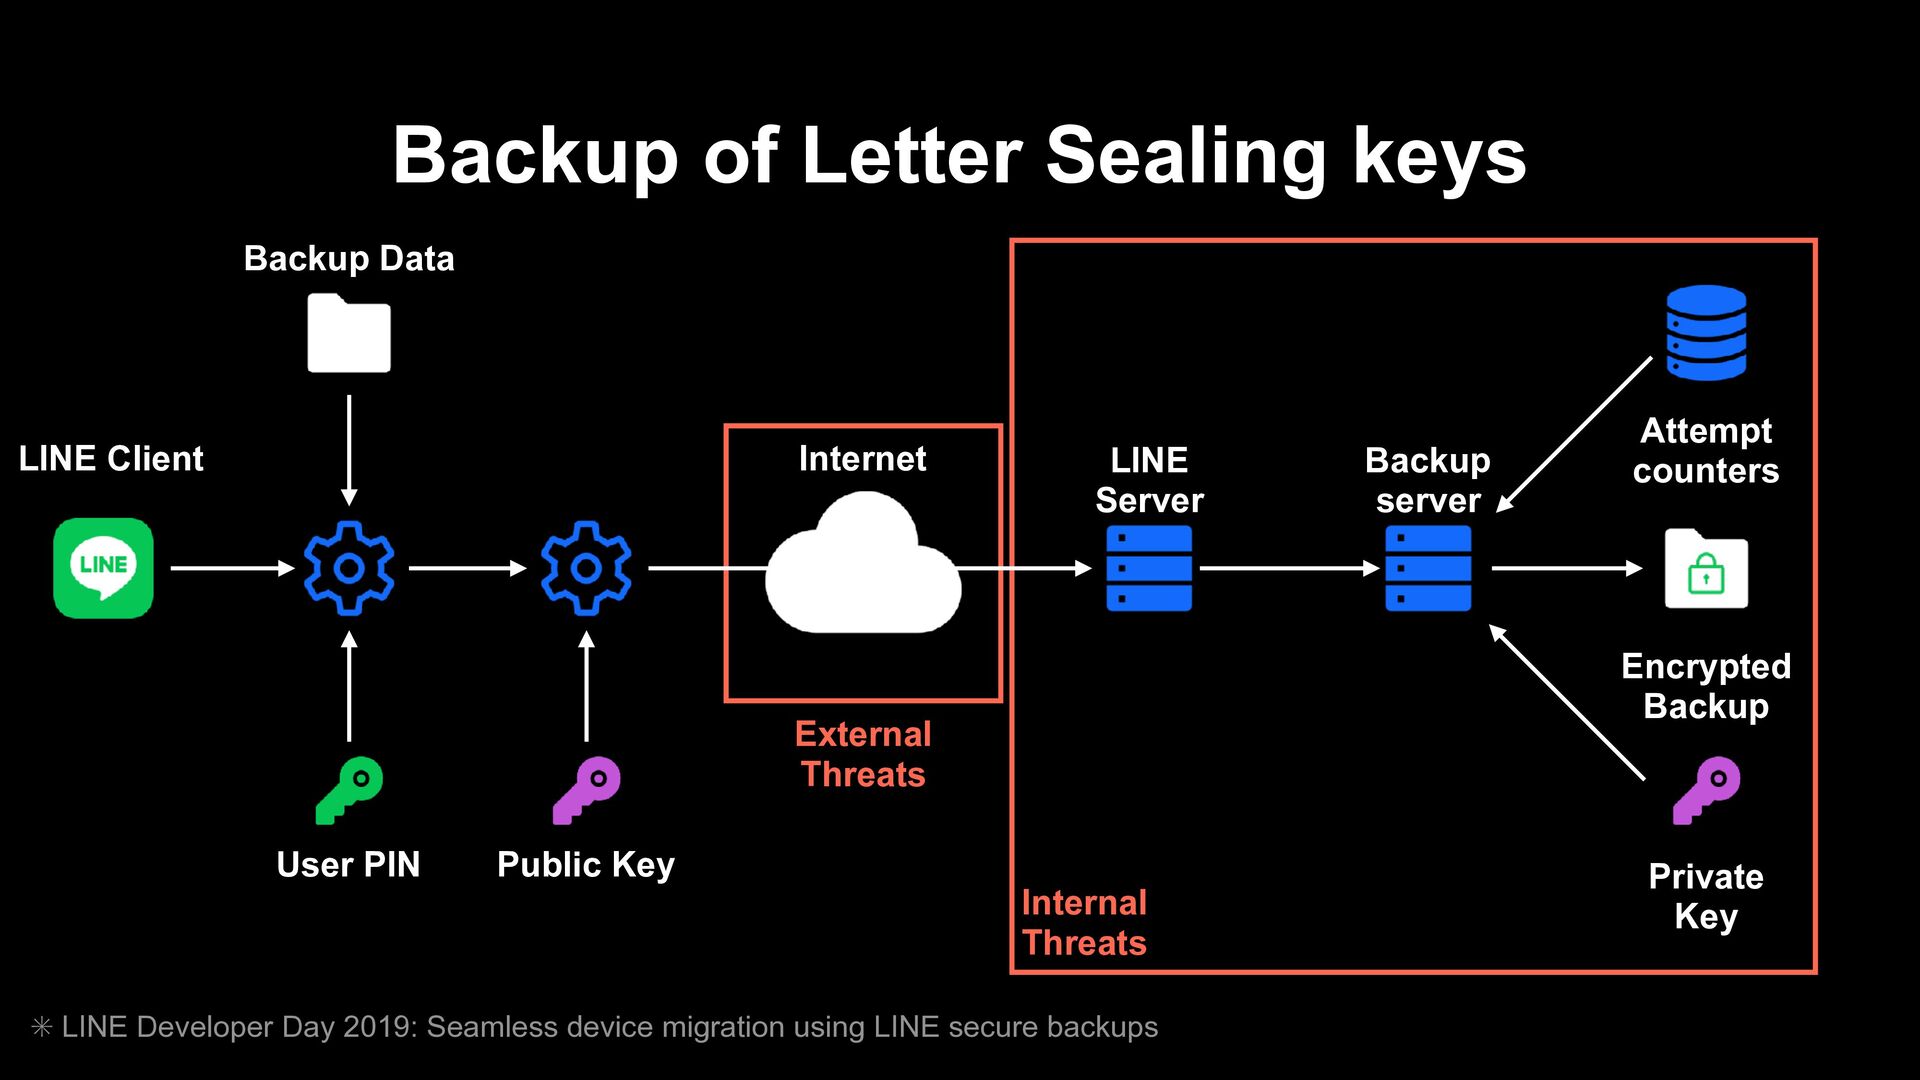
Internal Threats External Threats Backup of Letter Sealing keys ✳
LINE Developer Day 2019: Seamless device migration using LINE secure backups LINE Client LINE Server Backup server Encrypted Backup Internet User PIN Public Key Private Key Attempt counters Backup Data -
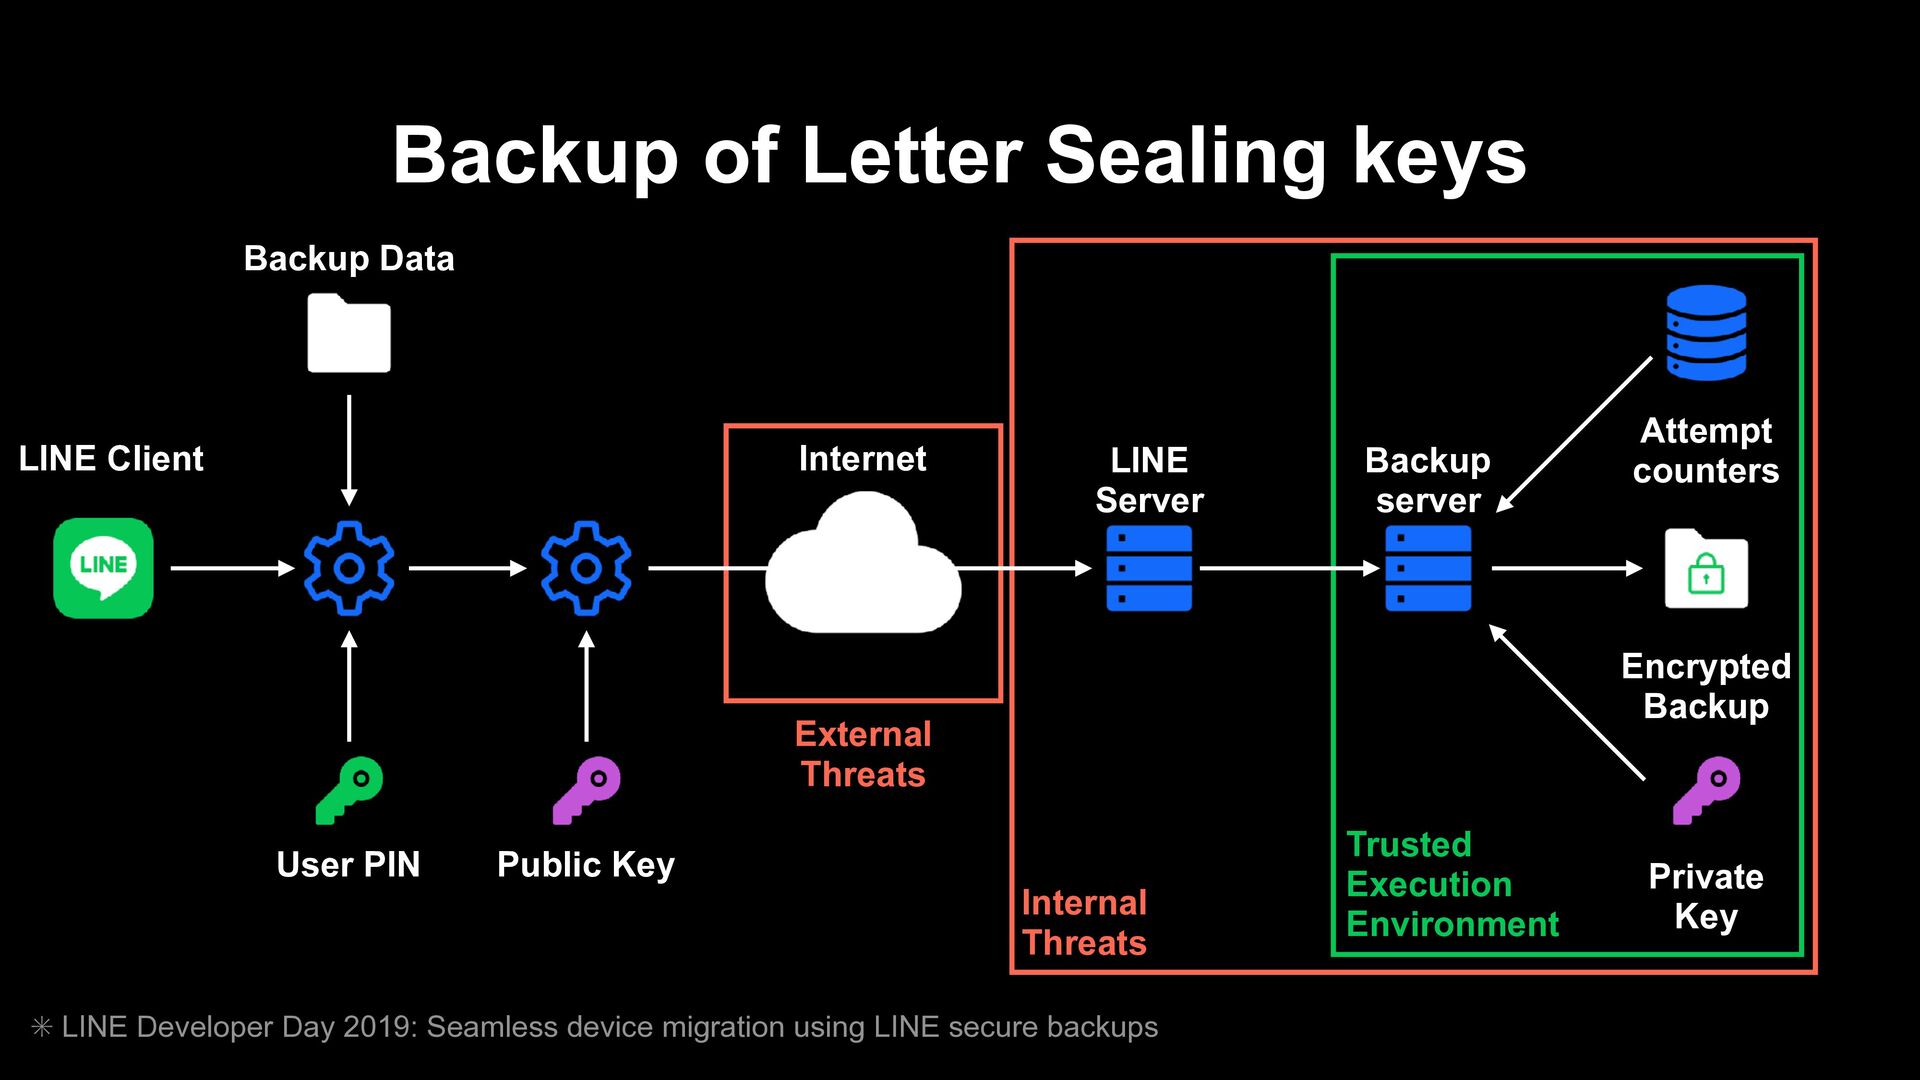
Trusted Execution Environment Internal Threats External Threats Backup of Letter
Sealing keys ✳ LINE Developer Day 2019: Seamless device migration using LINE secure backups LINE Client LINE Server Backup server Encrypted Backup Internet User PIN Public Key Private Key Attempt counters Backup Data -
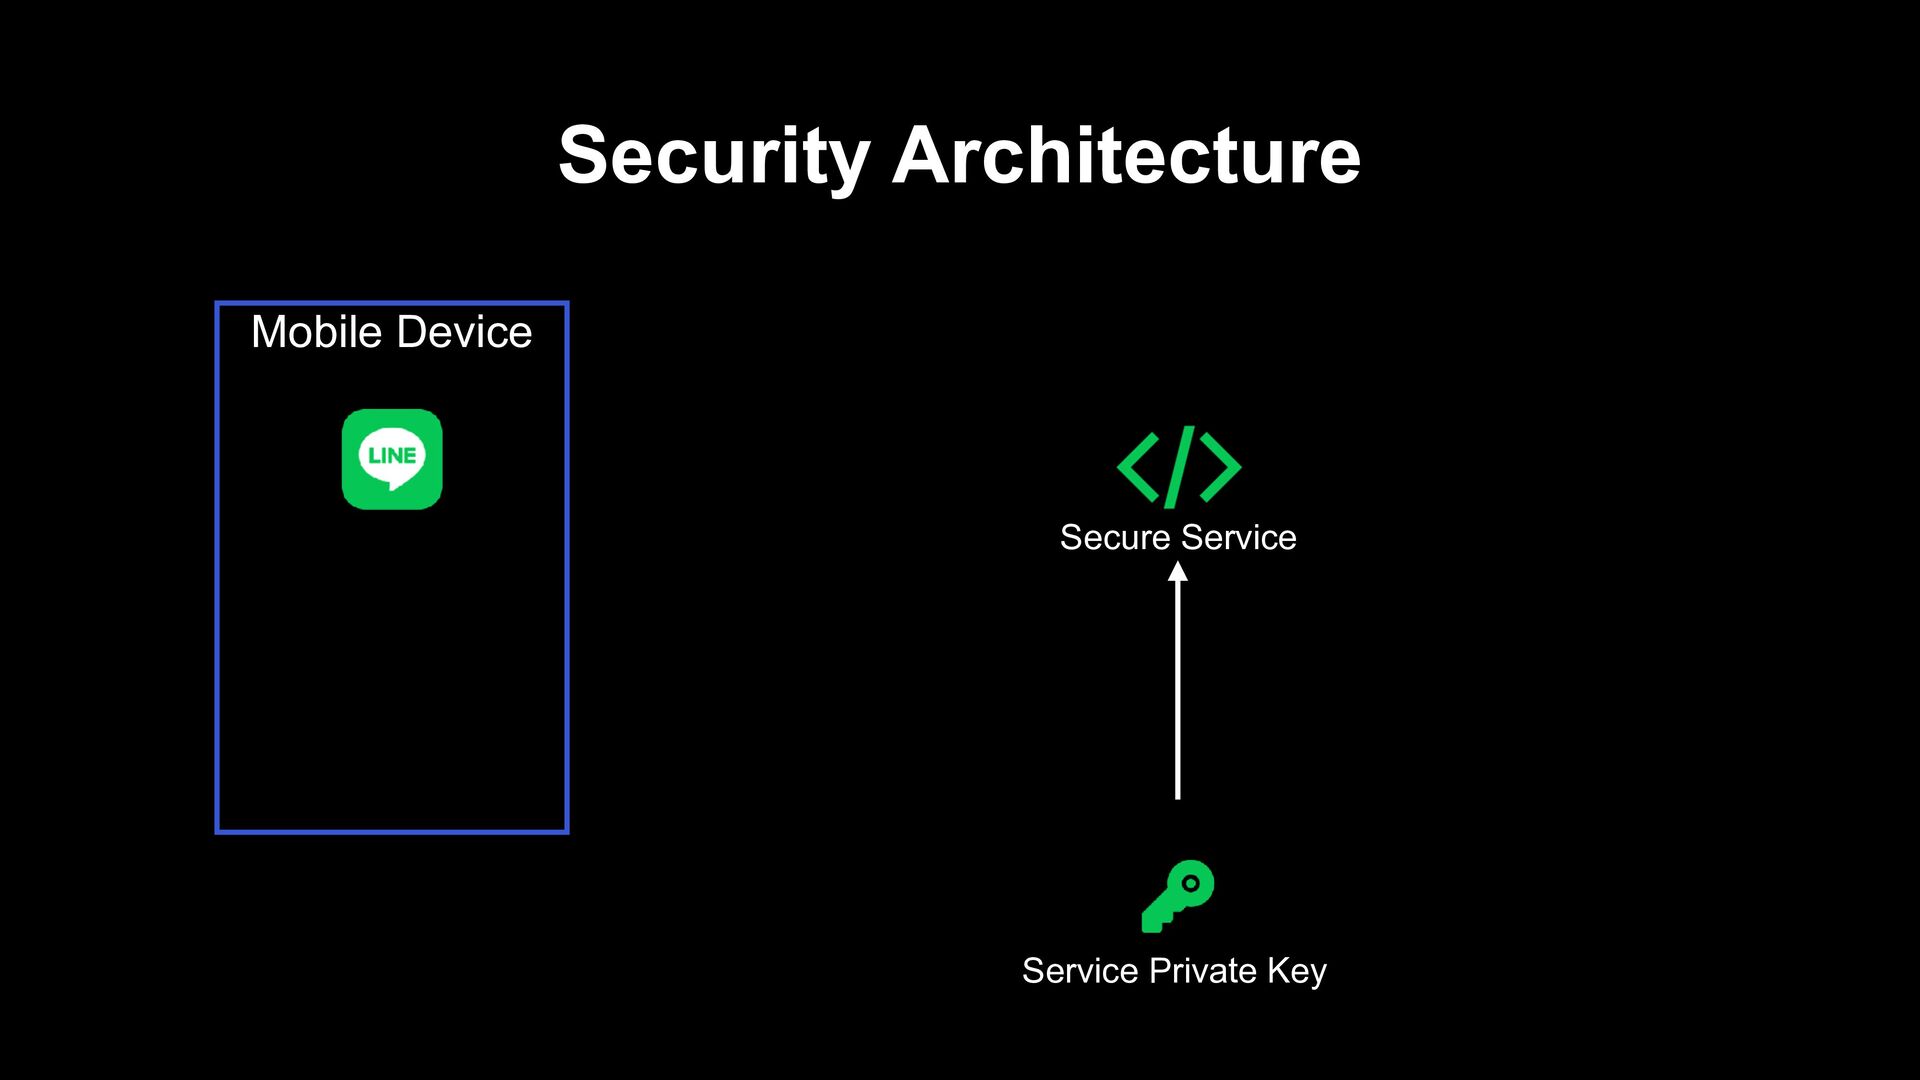
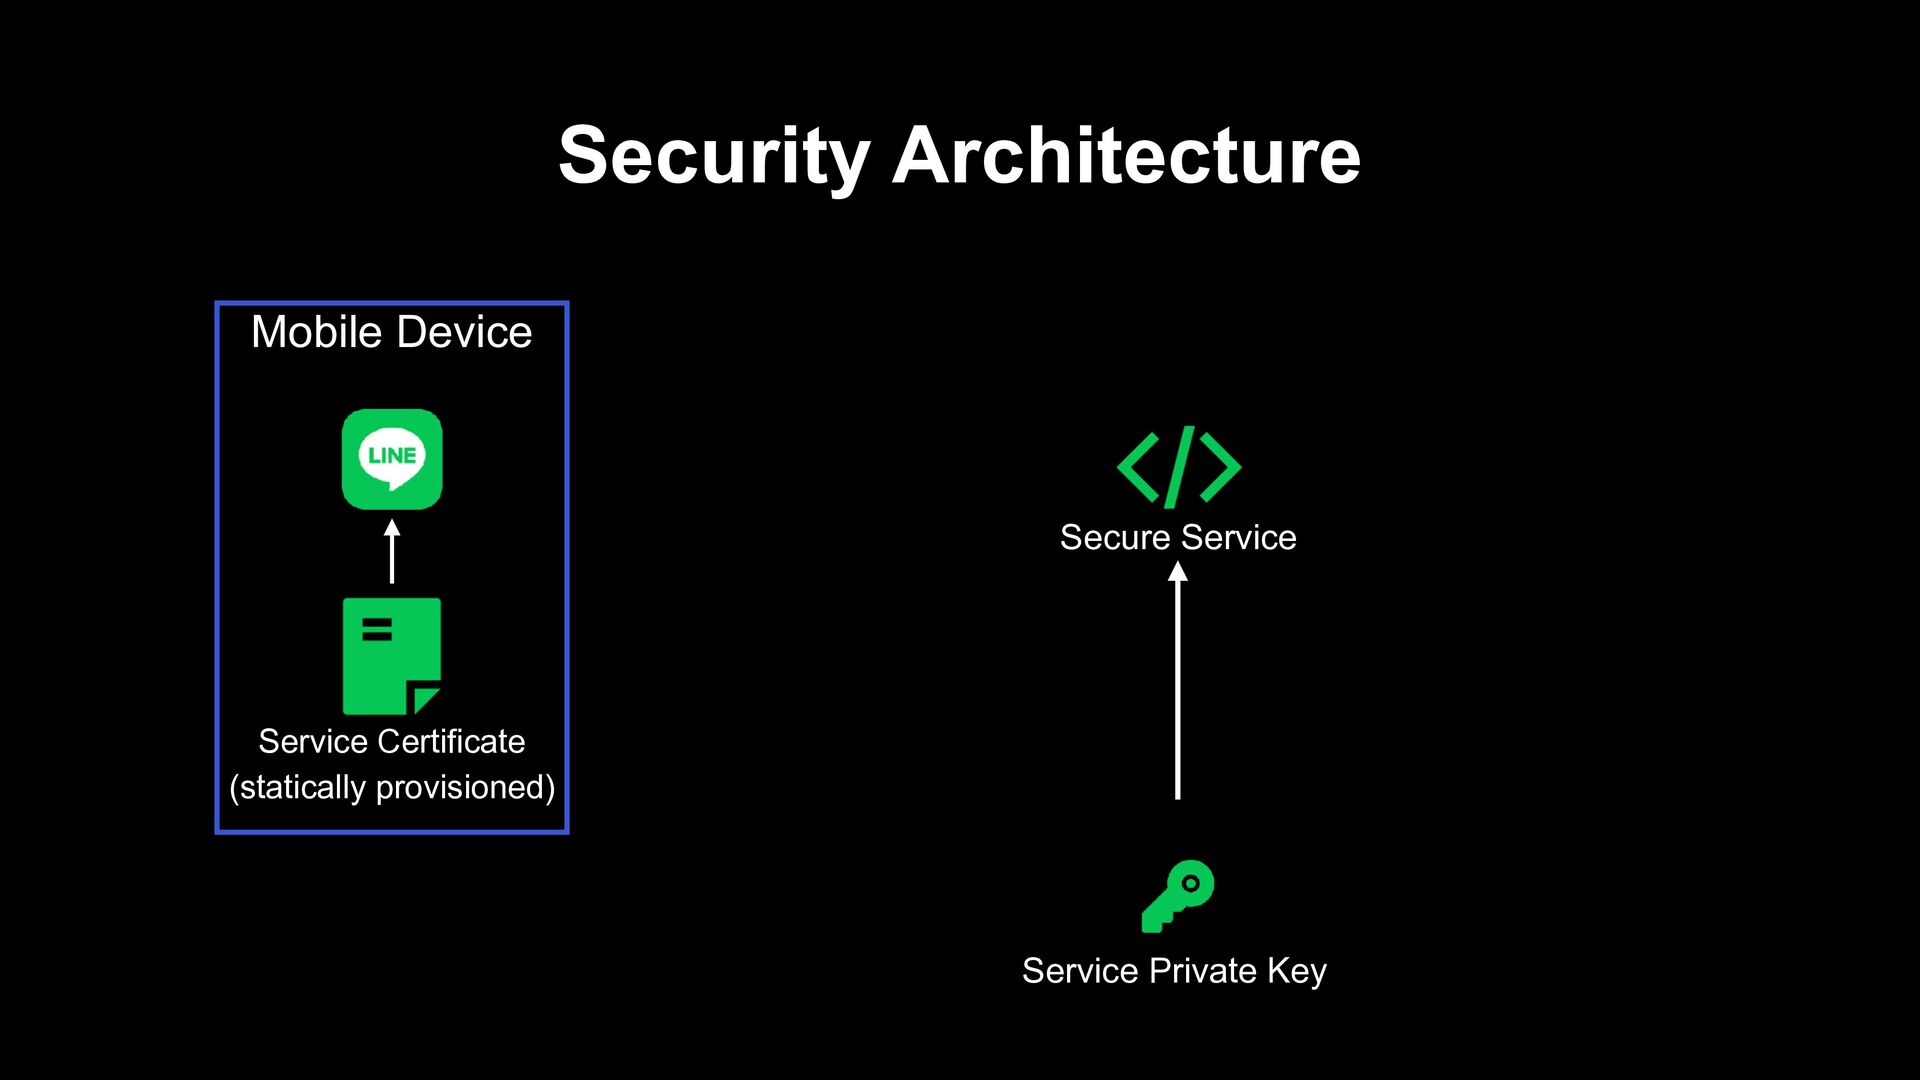
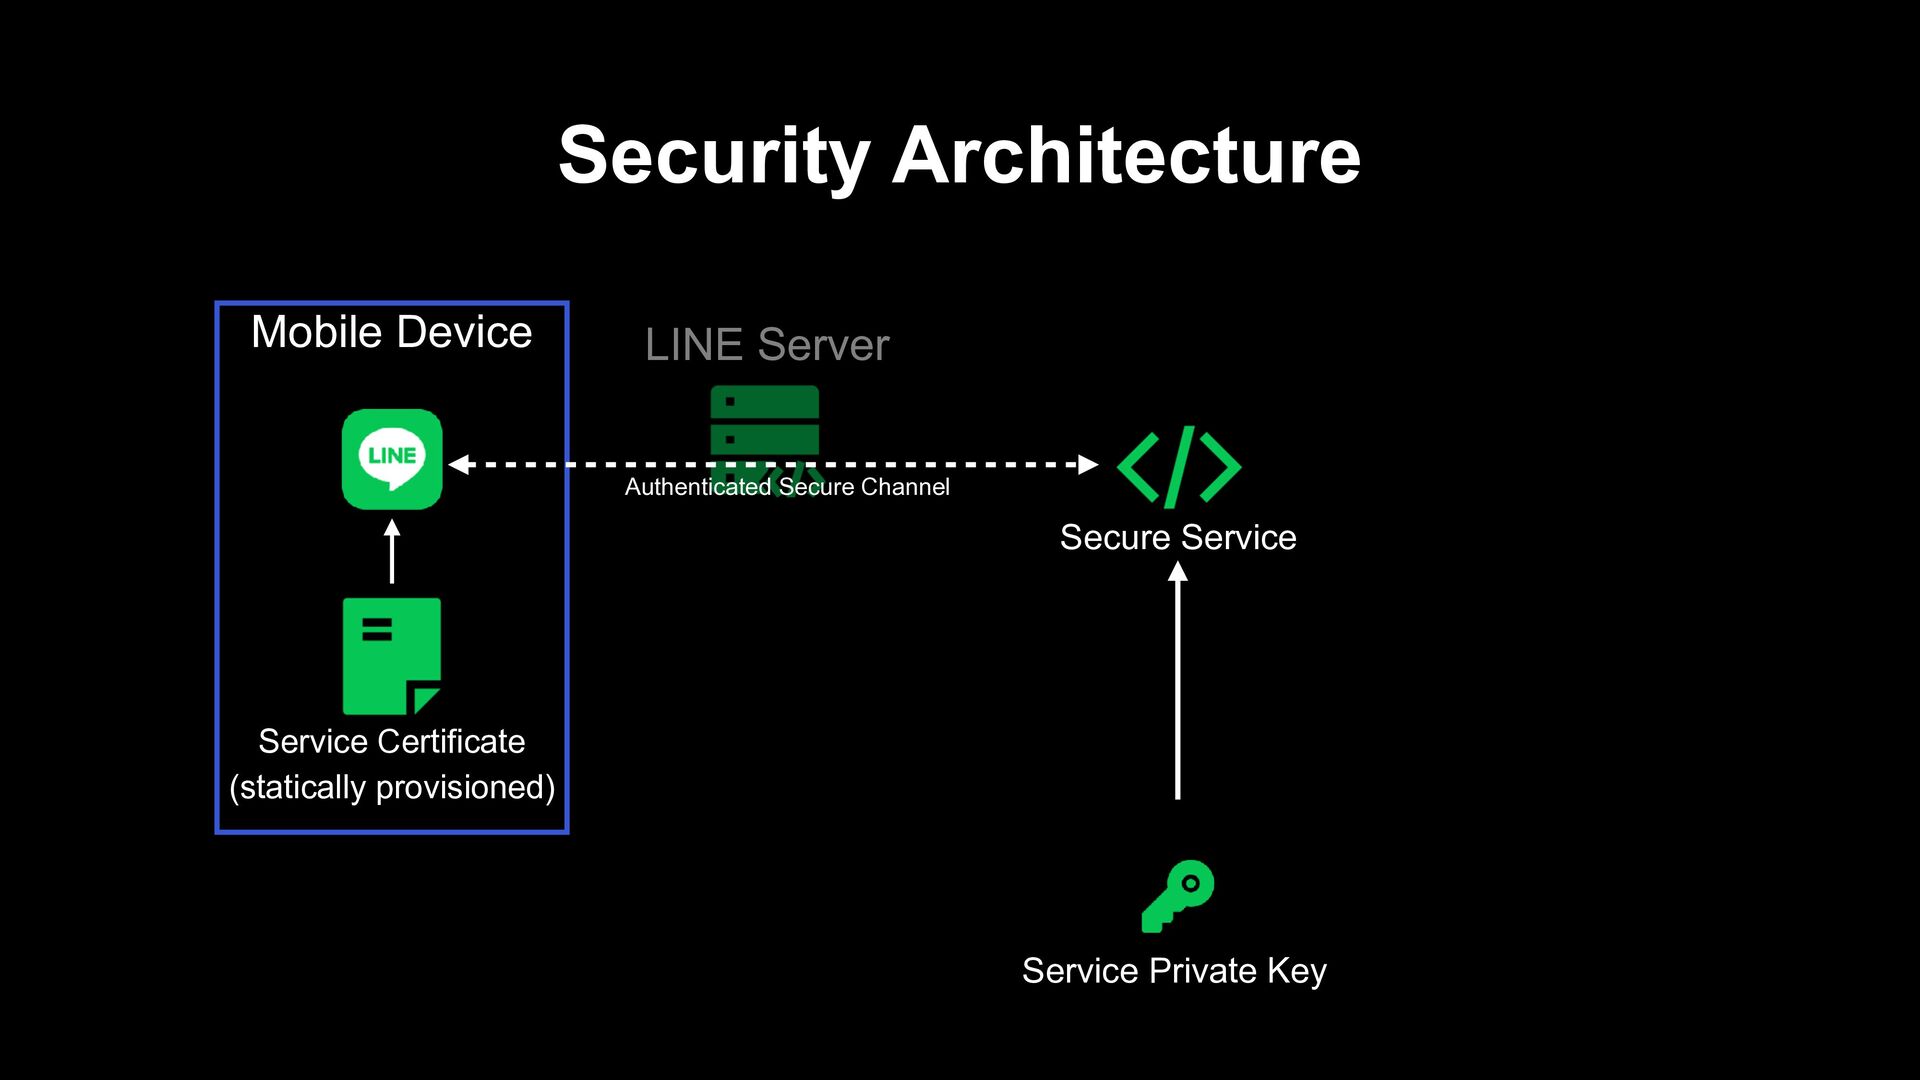
Security Architecture Mobile Device Service Certificate (statically provisioned) Secure Service
Service Private Key LINE Server Authenticated Secure Channel -
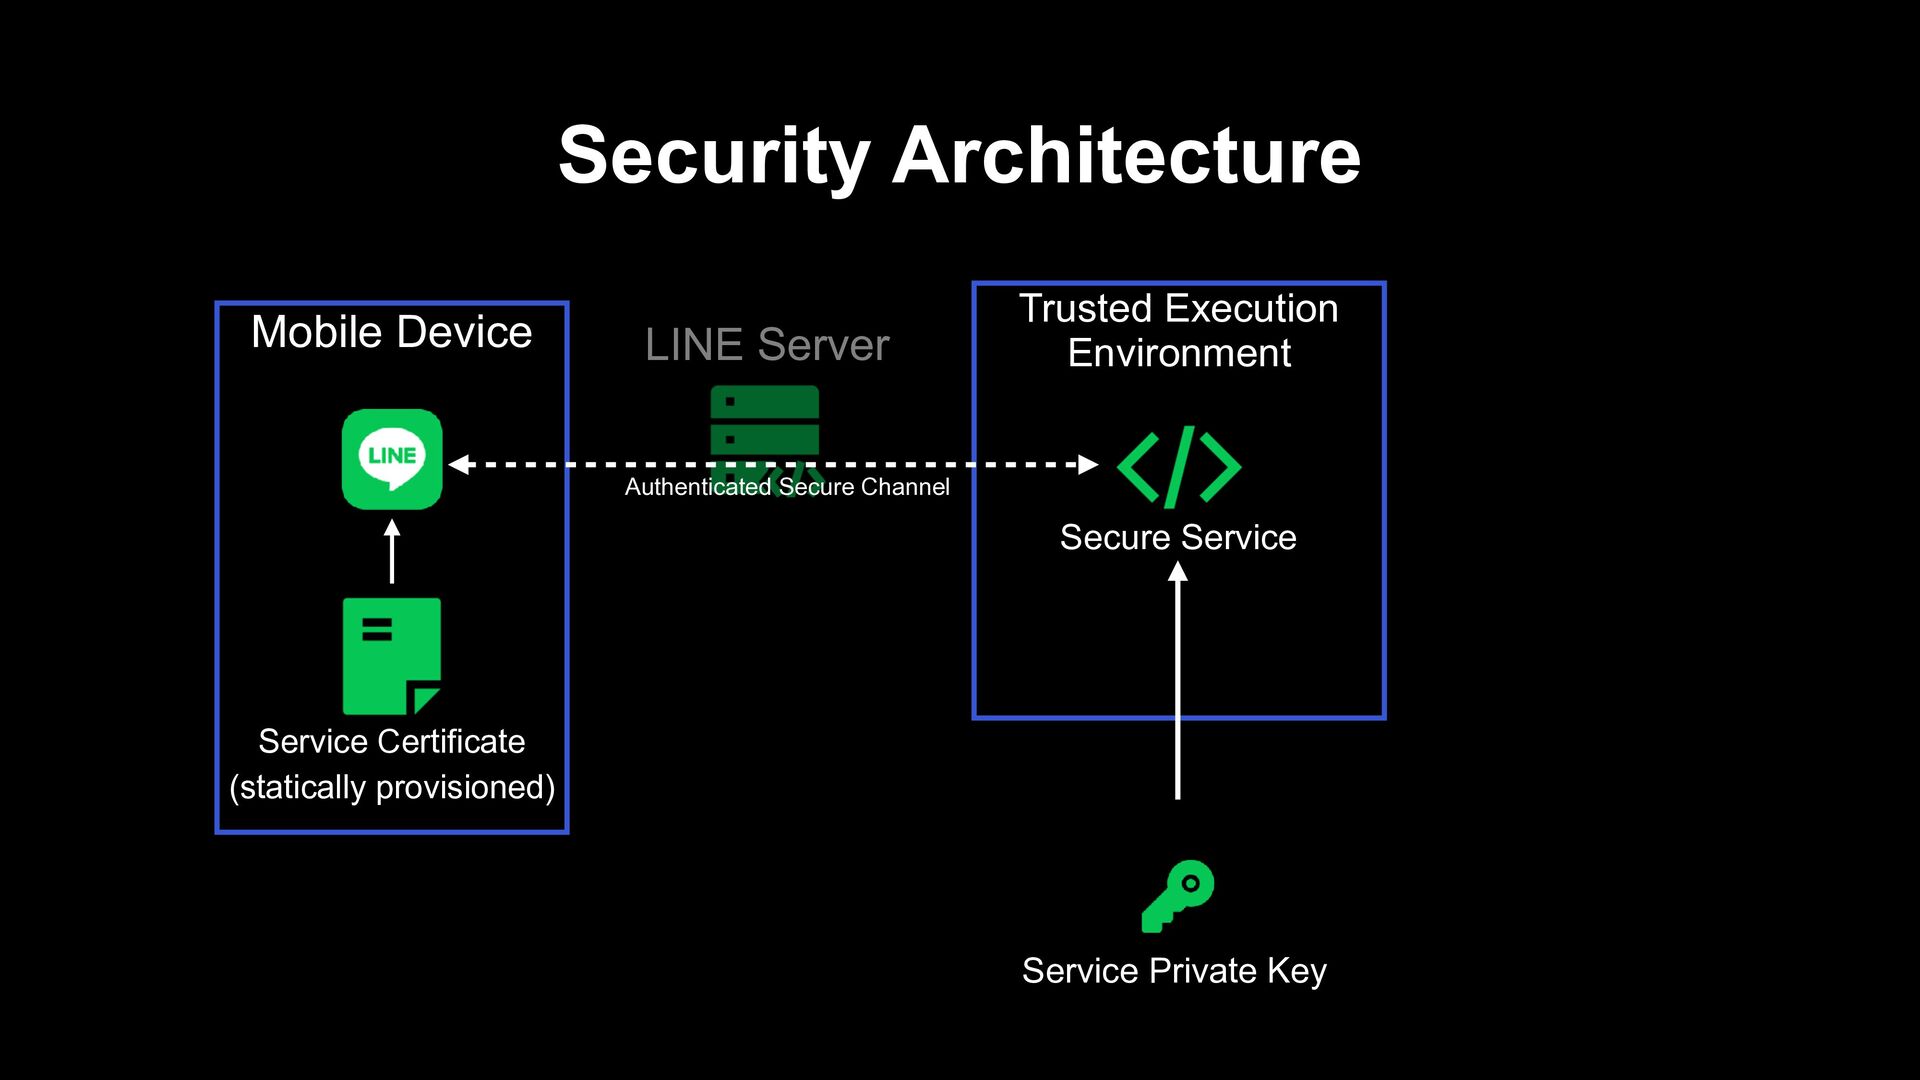
Security Architecture Mobile Device Service Certificate (statically provisioned) Trusted Execution
Environment Secure Service Service Private Key LINE Server Authenticated Secure Channel -
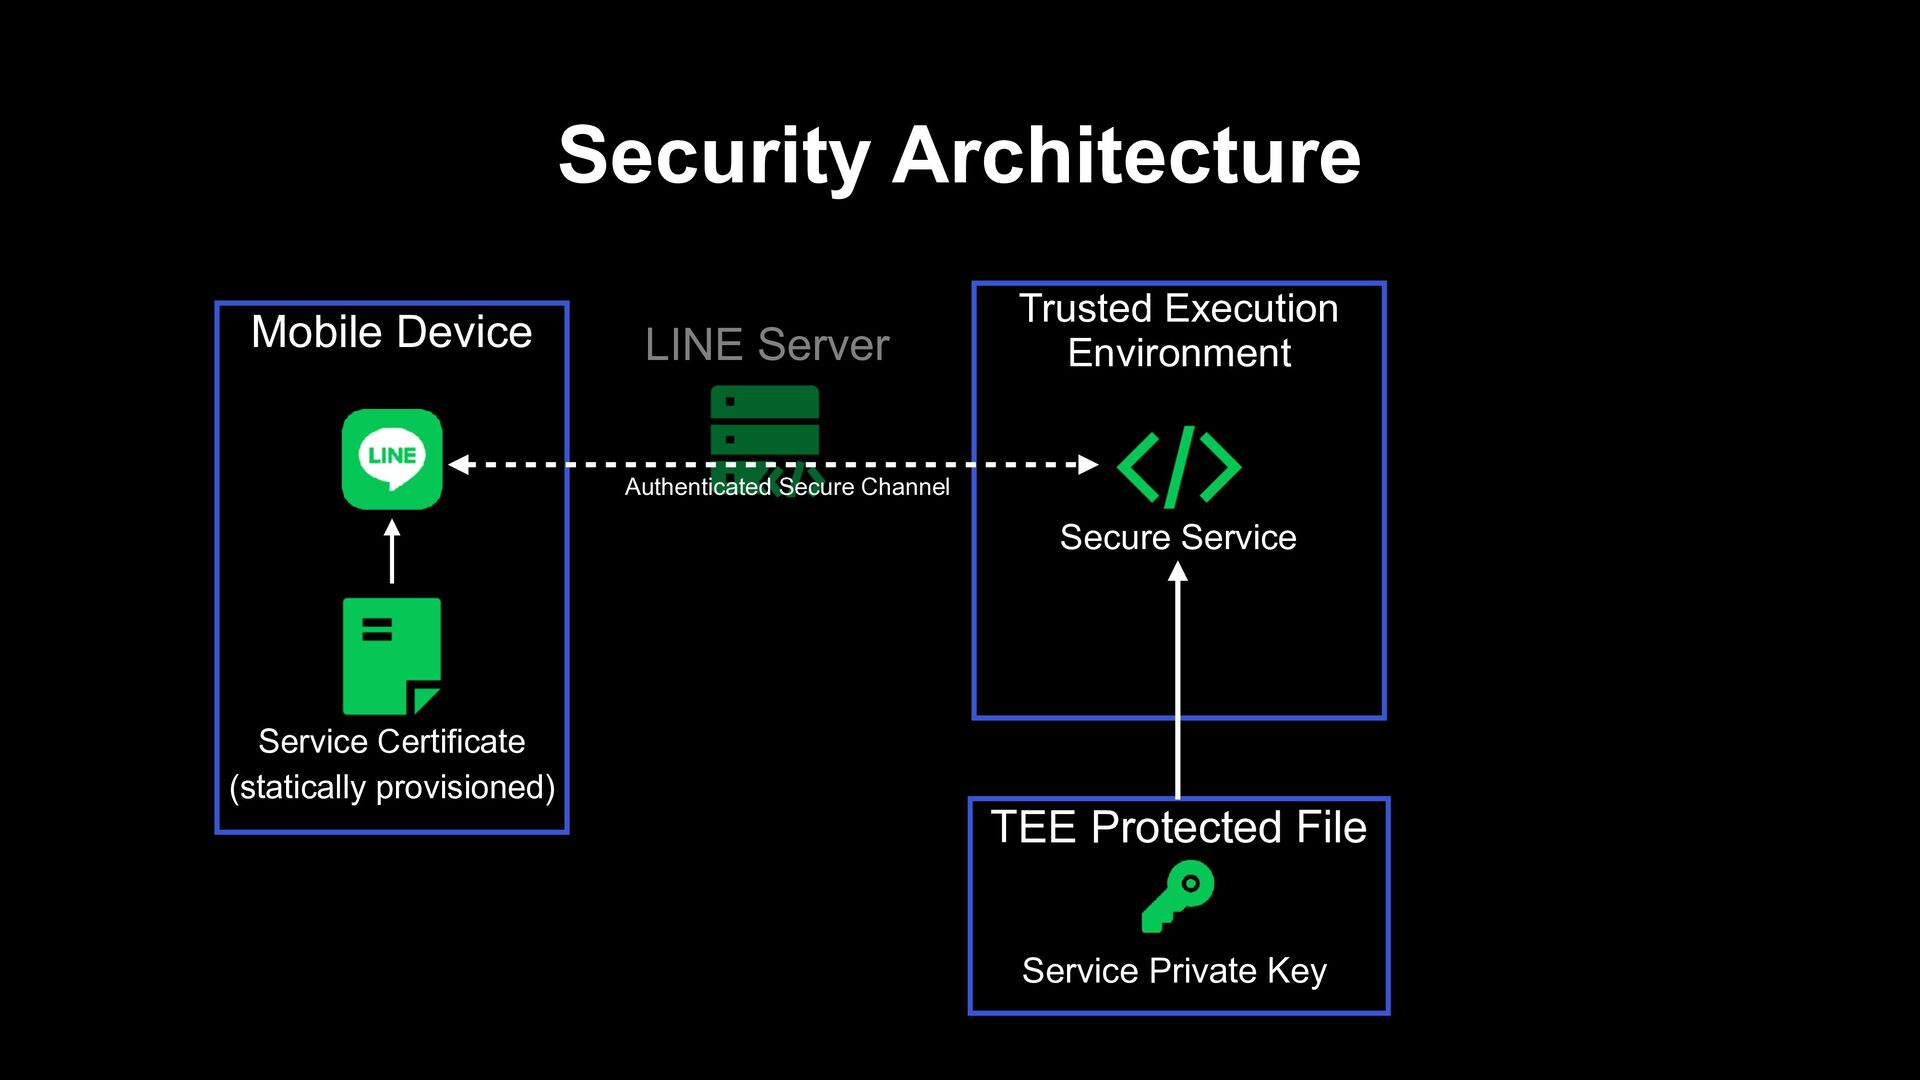
Security Architecture Mobile Device Service Certificate (statically provisioned) Trusted Execution
Environment Secure Service TEE Protected File Service Private Key LINE Server Authenticated Secure Channel -
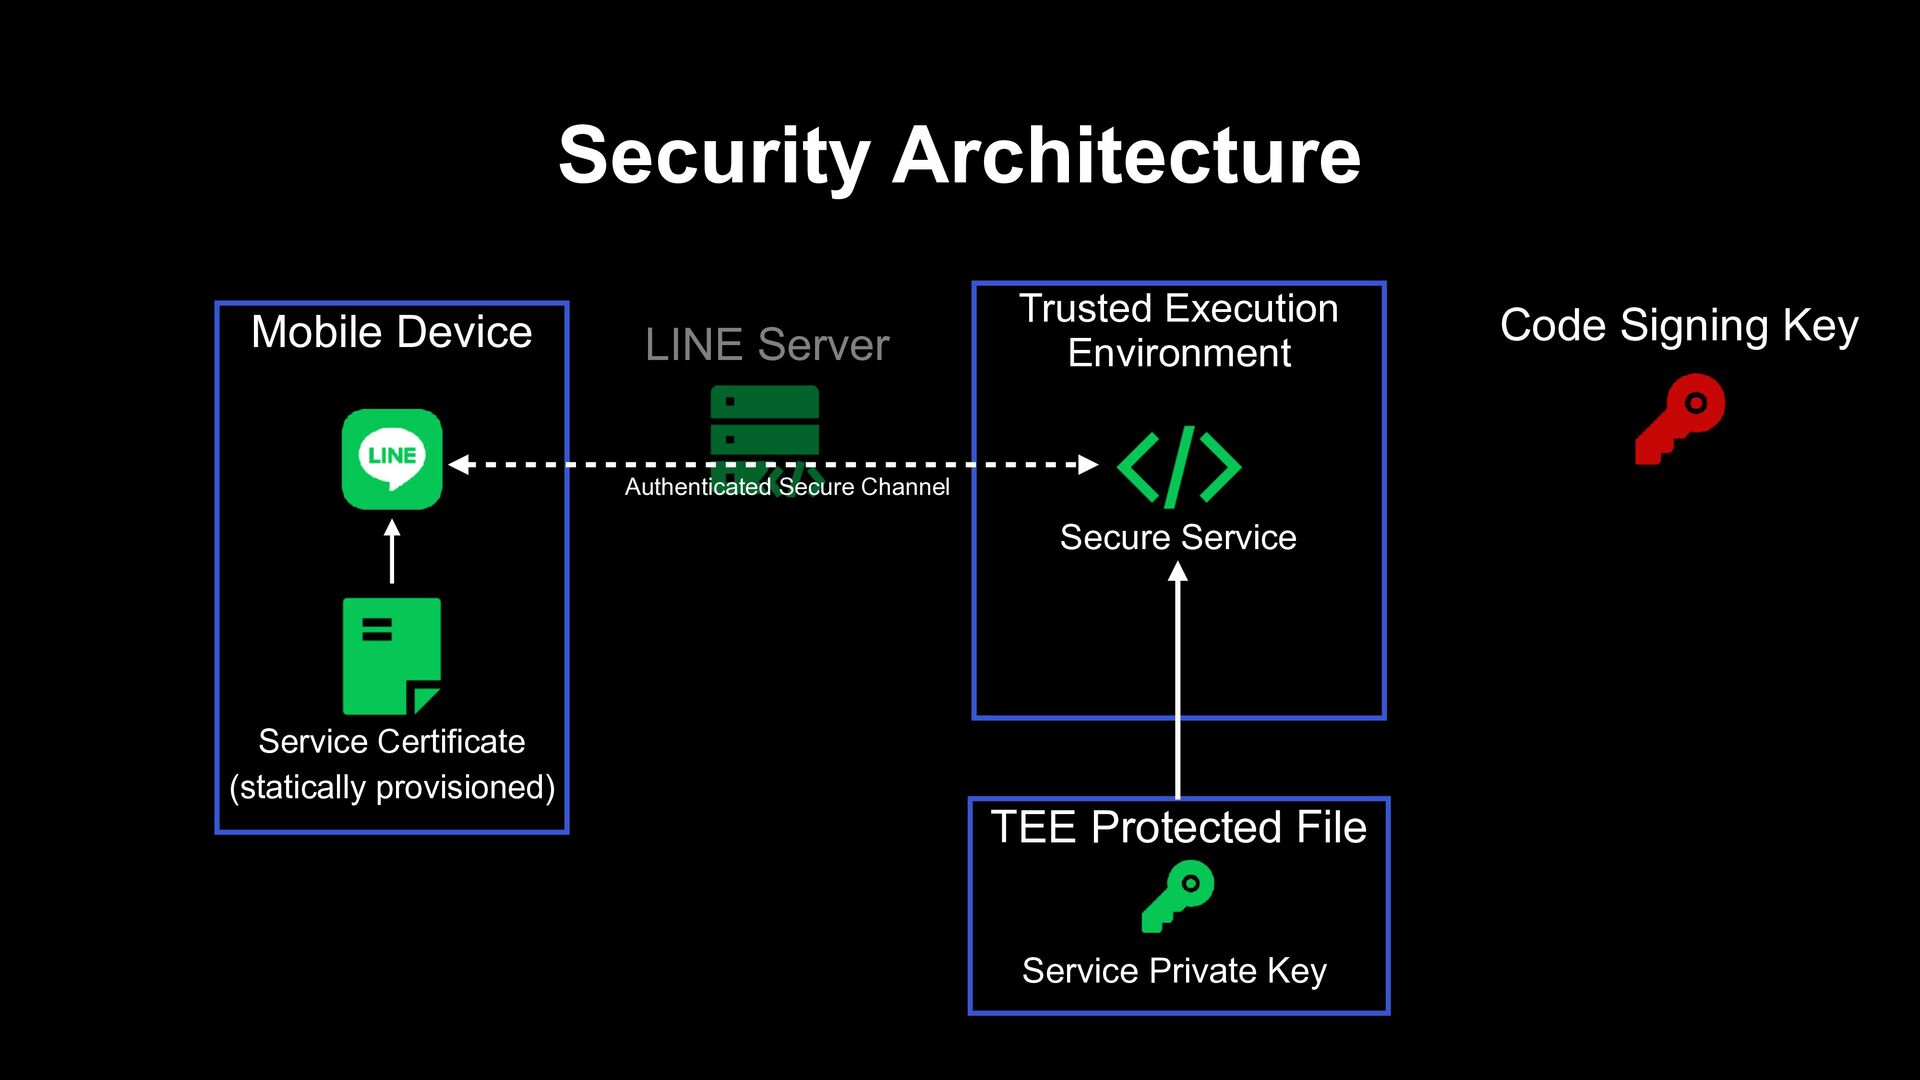
Security Architecture Mobile Device Service Certificate (statically provisioned) Trusted Execution
Environment Secure Service TEE Protected File Service Private Key Code Signing Key LINE Server Authenticated Secure Channel -
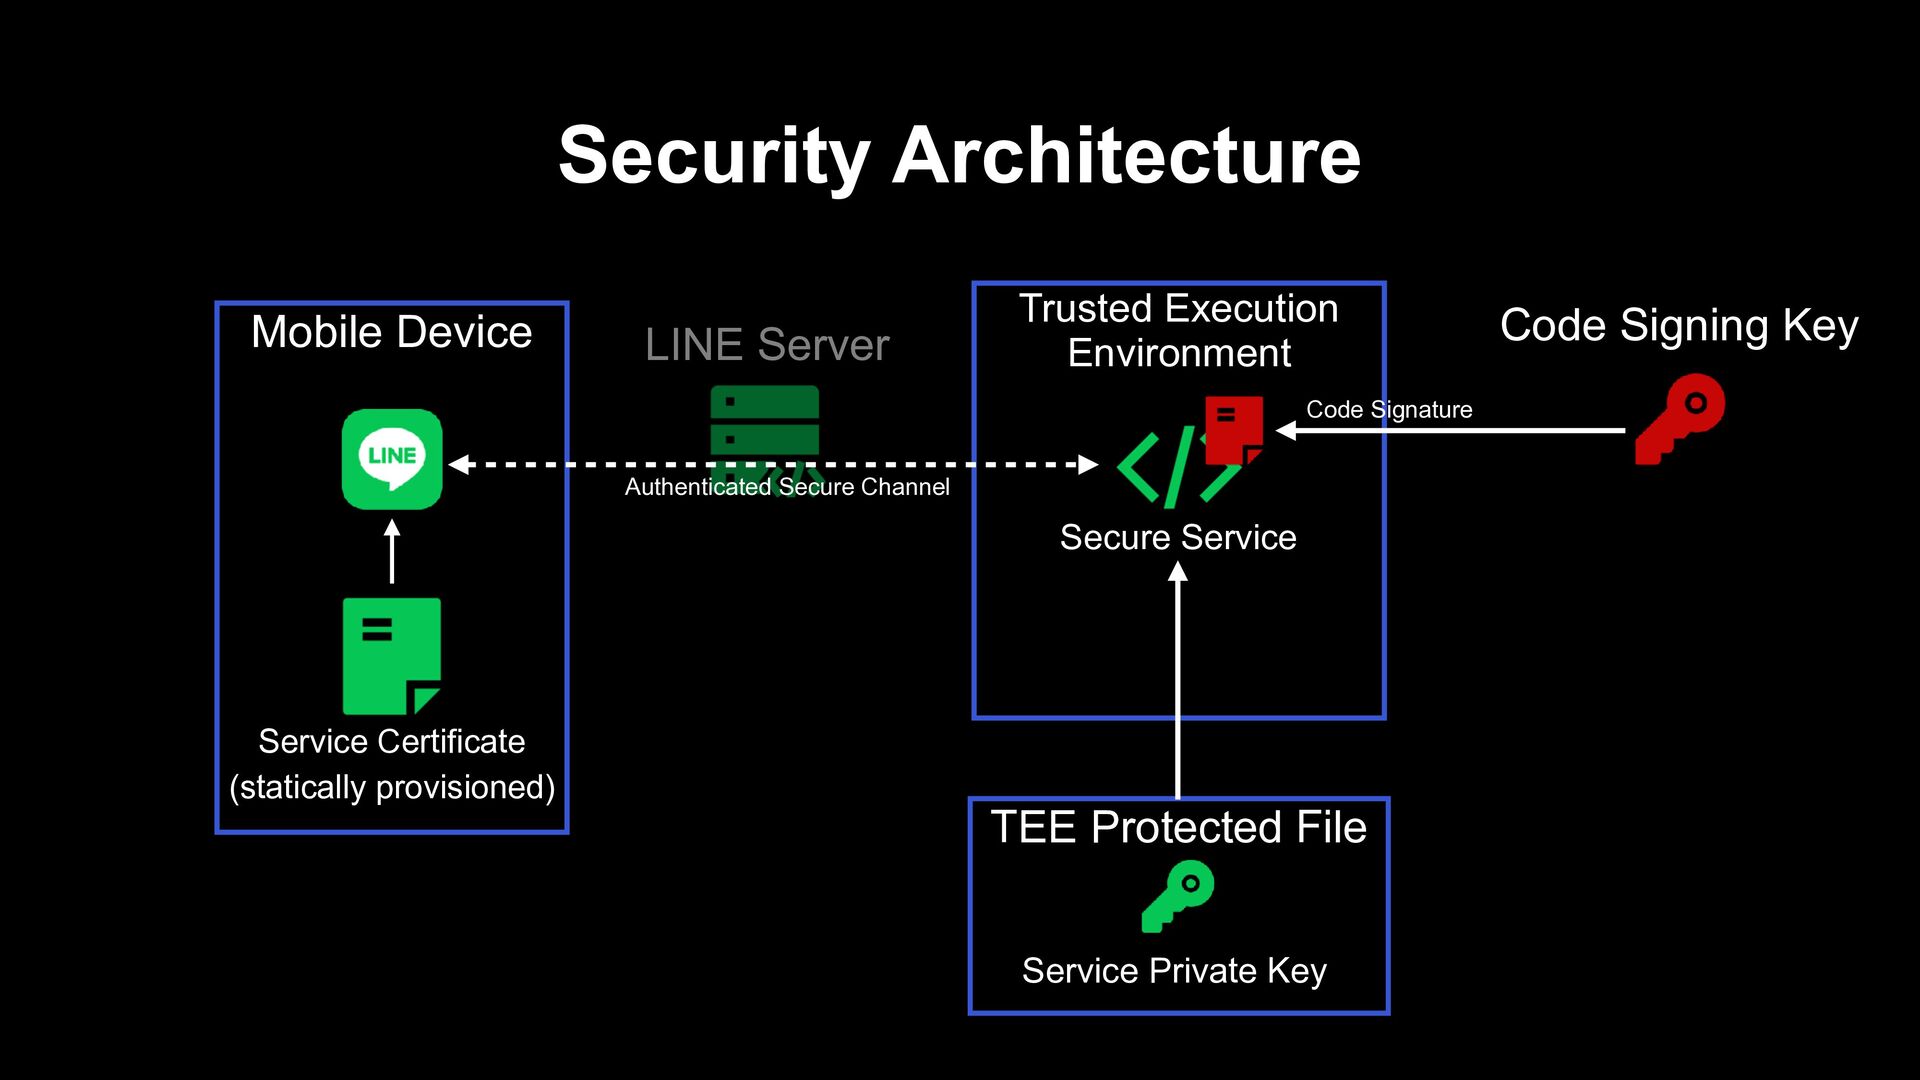
Security Architecture Mobile Device Service Certificate (statically provisioned) Trusted Execution
Environment Secure Service TEE Protected File Service Private Key Code Signing Key Code Signature LINE Server Authenticated Secure Channel -
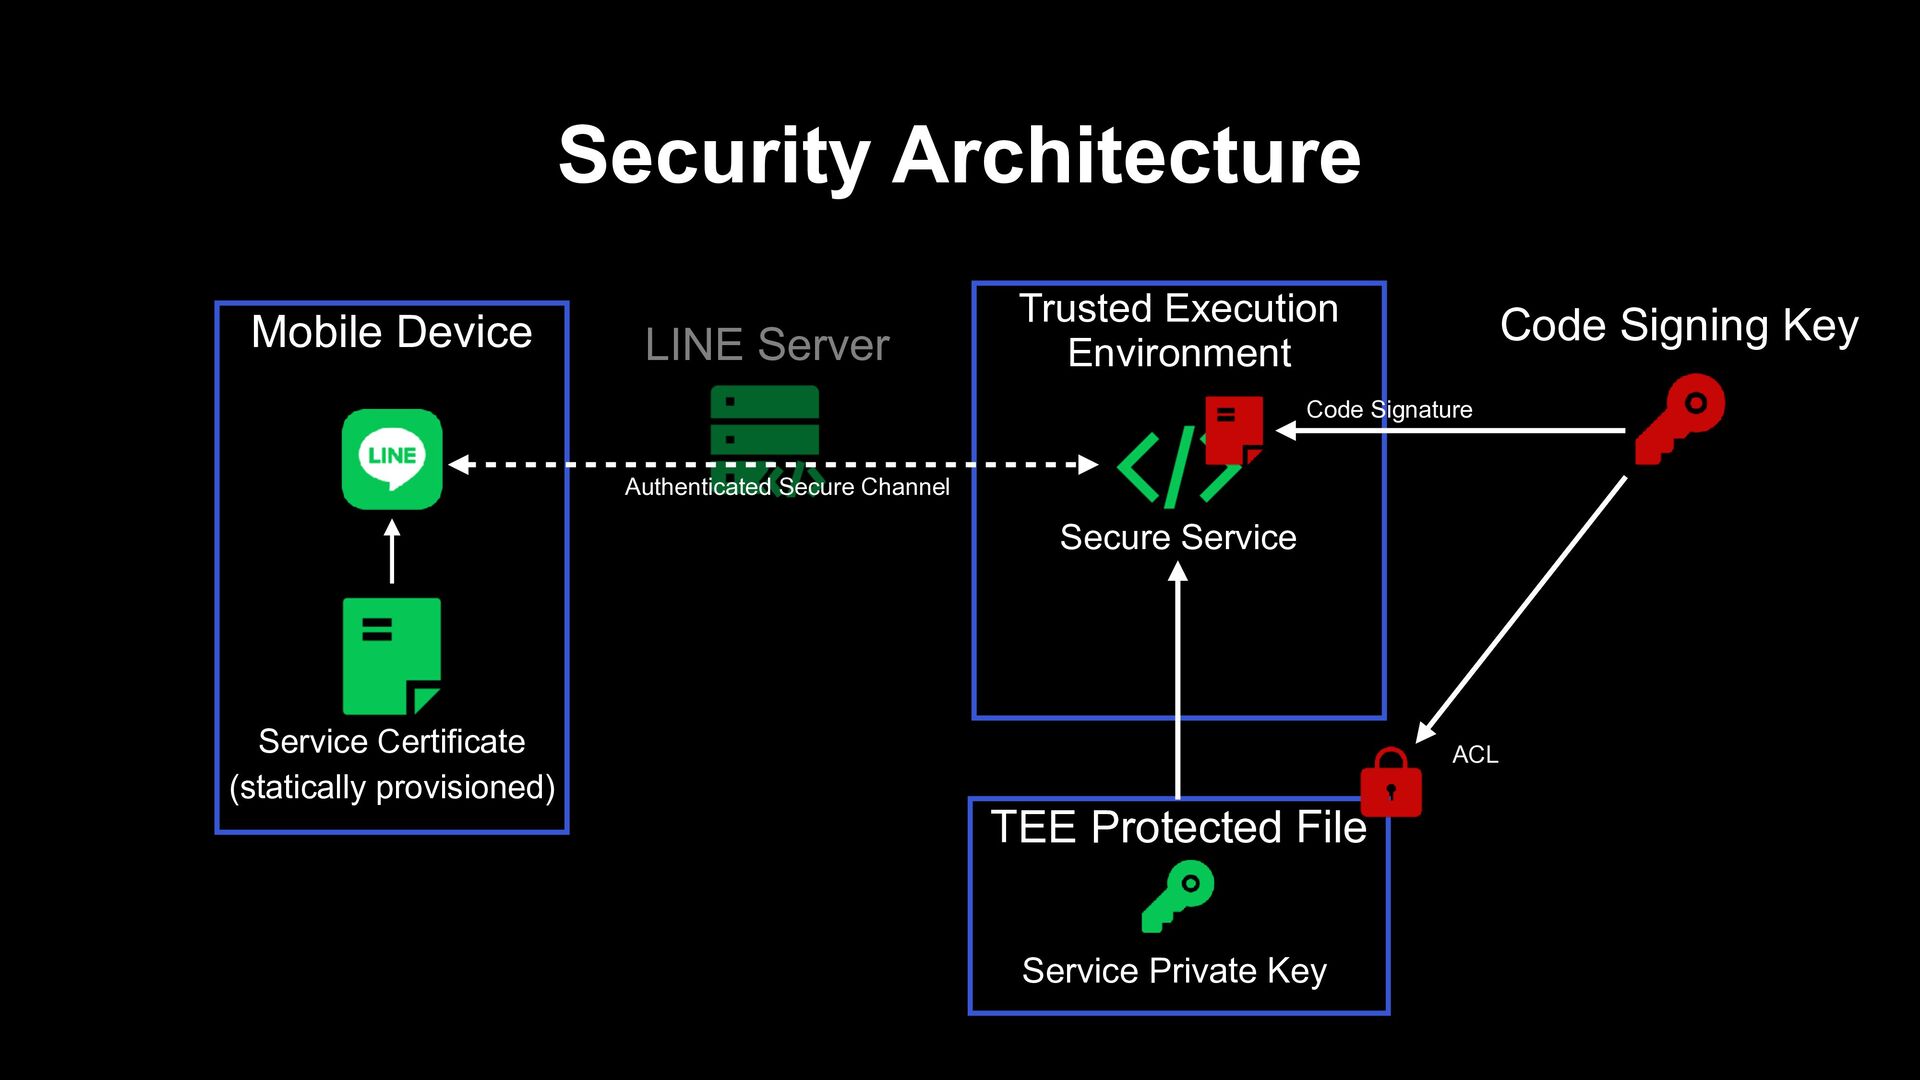
Security Architecture Mobile Device Service Certificate (statically provisioned) Trusted Execution
Environment Secure Service TEE Protected File Service Private Key Code Signing Key Code Signature ACL LINE Server Authenticated Secure Channel -
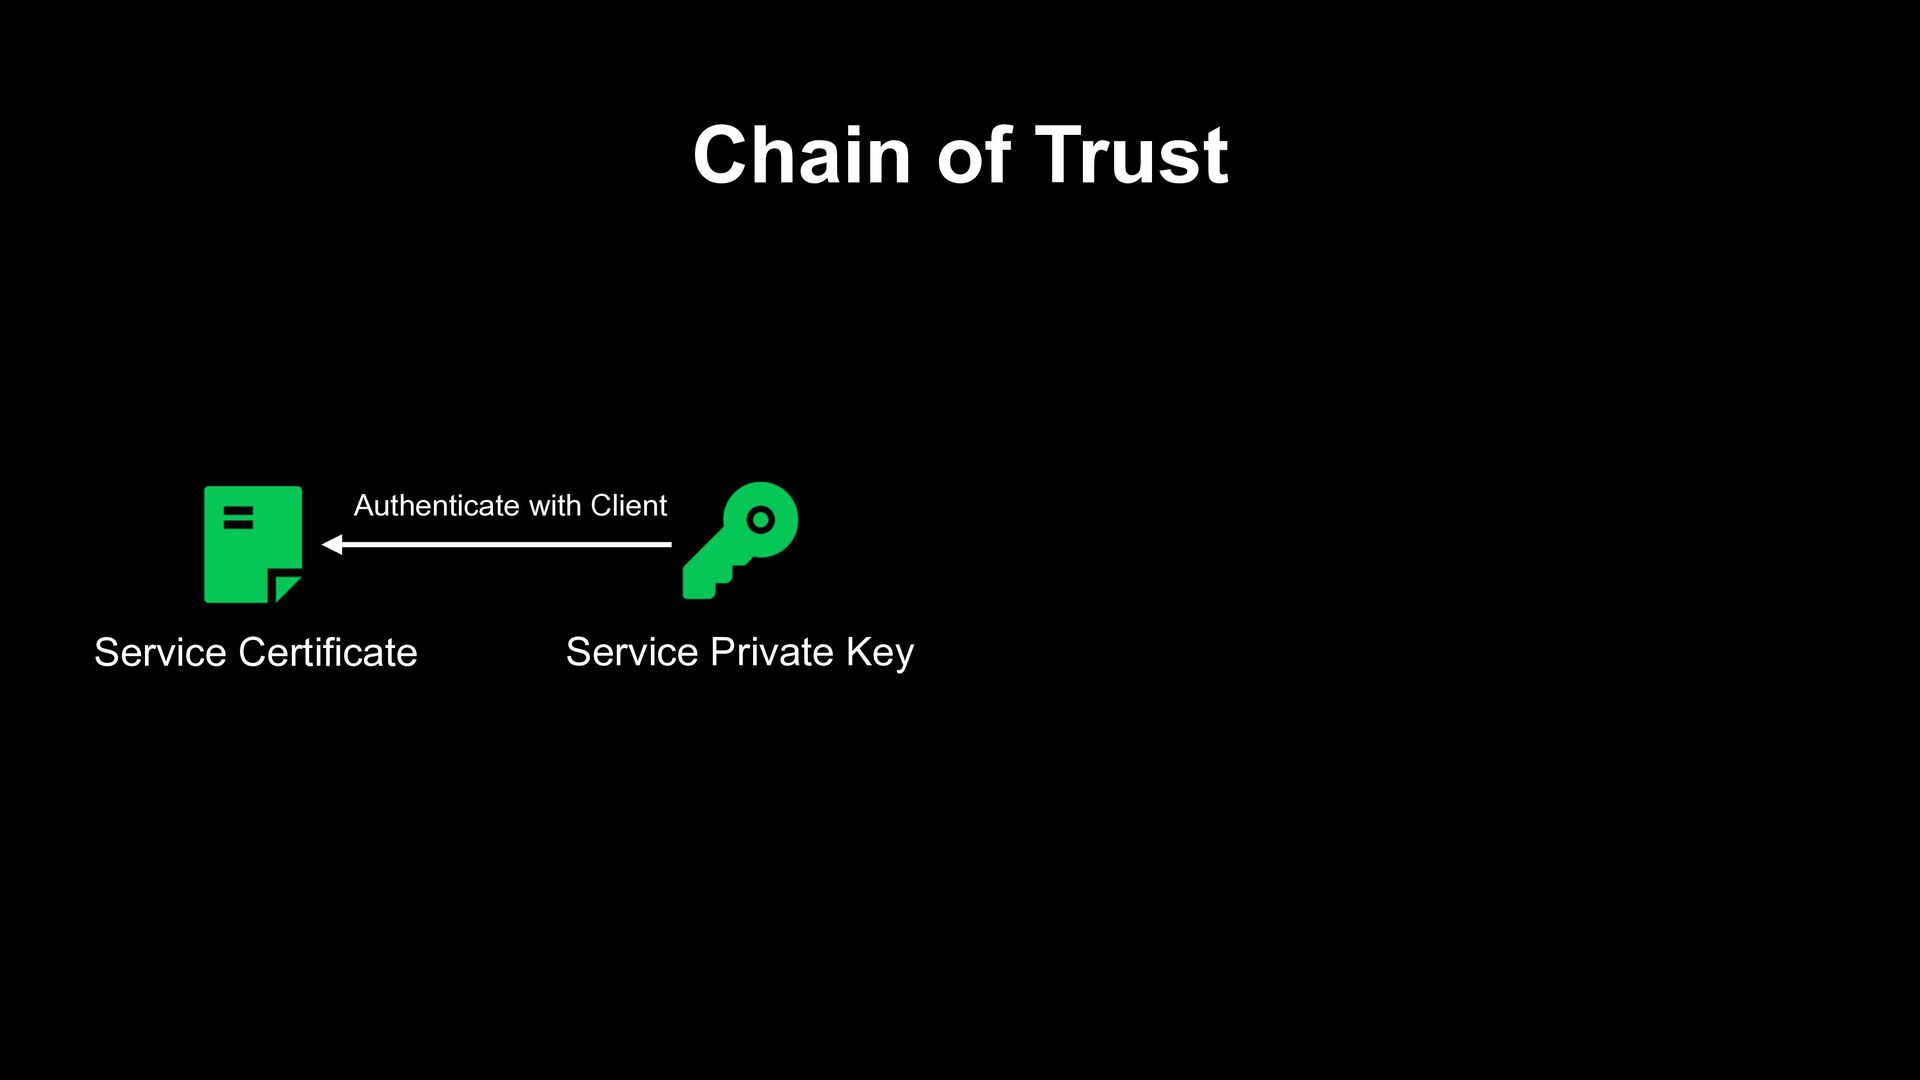
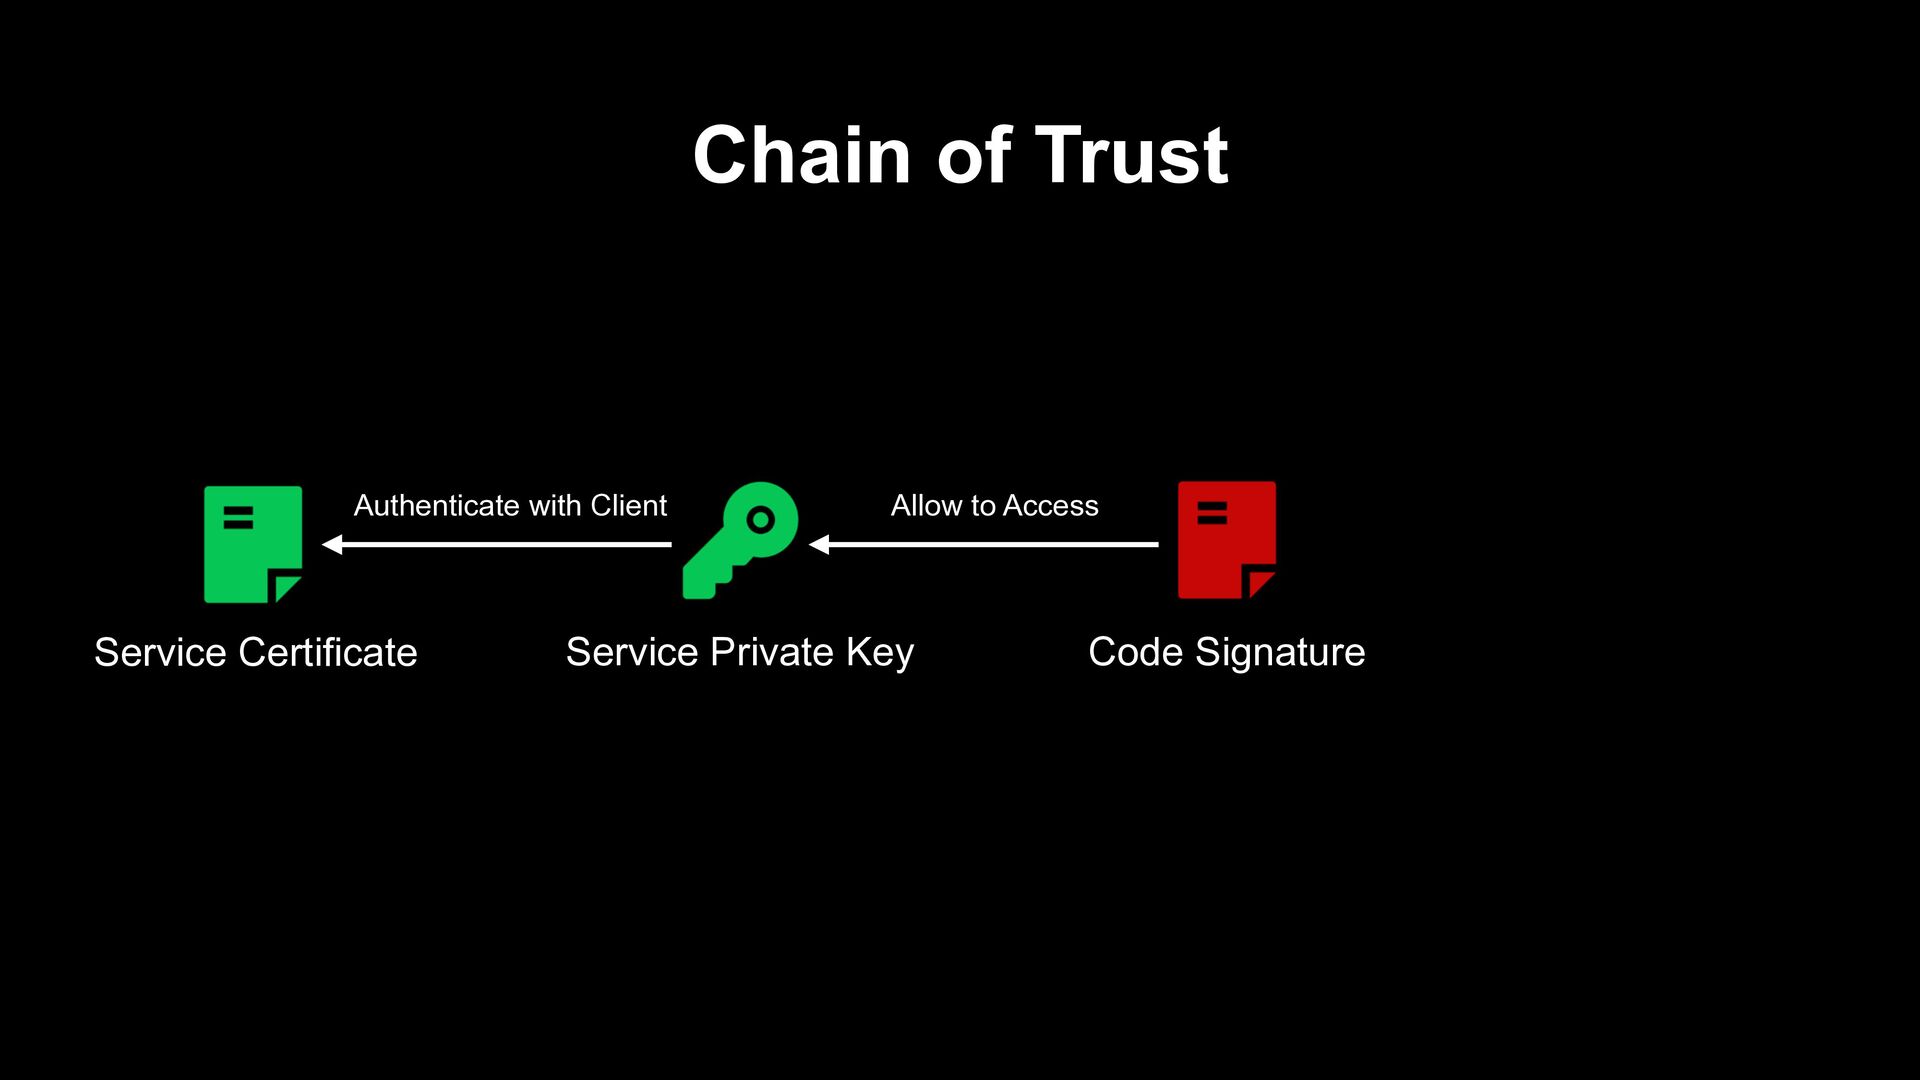
Chain of Trust Service Certificate Code Signature Allow to Access
Service Private Key Authenticate with Client -
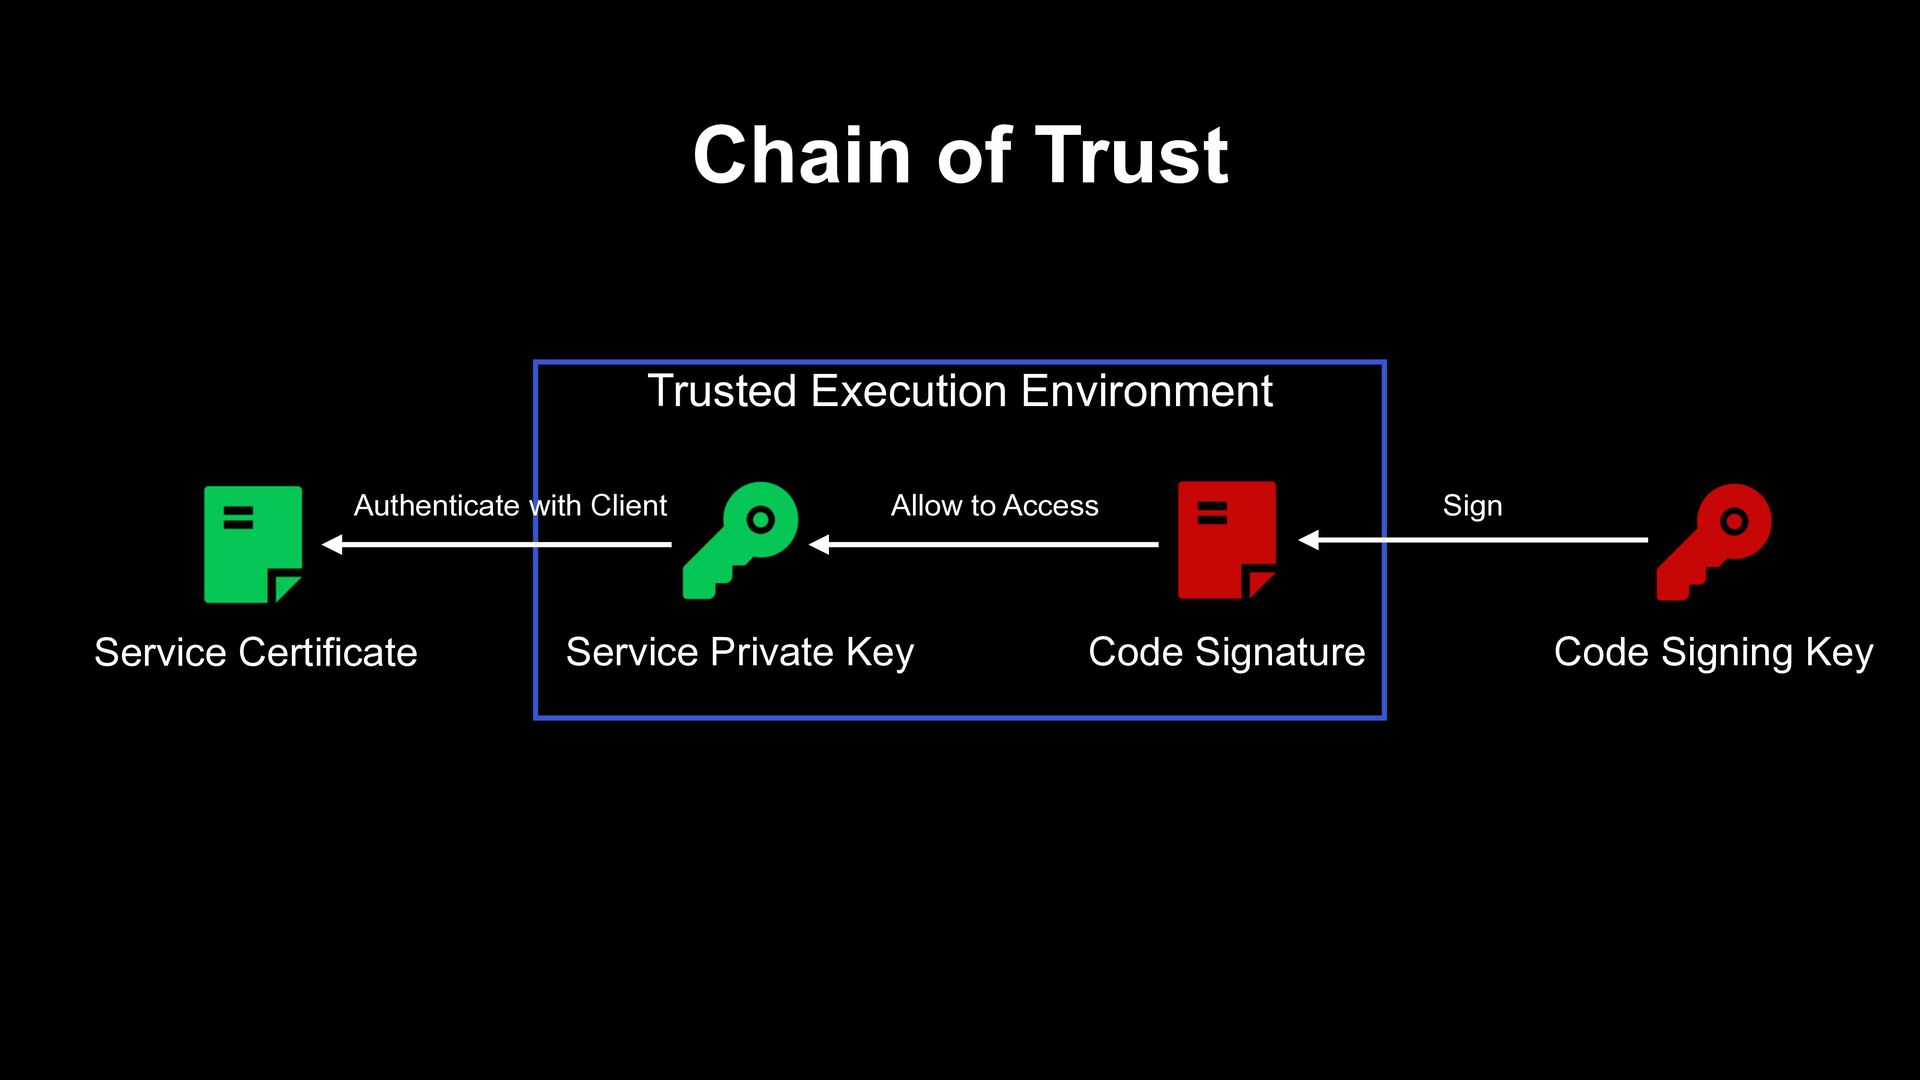
Chain of Trust Service Certificate Code Signing Key Sign Code
Signature Allow to Access Service Private Key Authenticate with Client -
Trusted Execution Environment Chain of Trust Service Certificate Code Signing
Key Sign Code Signature Allow to Access Service Private Key Authenticate with Client -
Root of Trust - Code signing key becomes the root
of trust - Only the code signing key has to be protected -
Root of Trust - Code signing key becomes the root
of trust - Only the code signing key has to be protected - Can be protected offline with a high level of physical security -
Root of Trust - Code signing key becomes the root
of trust - Only the code signing key has to be protected - Can be protected offline with a high level of physical security - Can also be destroyed -
Root of Trust - Code signing key becomes the root
of trust - Only the code signing key has to be protected - Can be protected offline with a high level of physical security - Can also be destroyed ➡ Security by immutability -
Trusted Execution Environment - Hardware support for cryptographic features -
Loading and executing signed code -
Trusted Execution Environment - Hardware support for cryptographic features -
Loading and executing signed code - Guarantee integrity and confidentiality -
Trusted Execution Environment - Hardware support for cryptographic features -
Loading and executing signed code - Guarantee integrity and confidentiality - Many implementations: -
Trusted Execution Environment - Hardware support for cryptographic features -
Loading and executing signed code - Guarantee integrity and confidentiality - Many implementations: - CPU feature: ARM® TrustZone®, Intel® SGX, … -
Trusted Execution Environment - Hardware support for cryptographic features -
Loading and executing signed code - Guarantee integrity and confidentiality - Many implementations: - CPU feature: ARM® TrustZone®, Intel® SGX, … - Dedicated chips: Apple® Secure Enclave, Google® Titan -
Trusted Execution Environment - Hardware support for cryptographic features -
Loading and executing signed code - Guarantee integrity and confidentiality - Many implementations: - CPU feature: ARM® TrustZone®, Intel® SGX, … - Dedicated chips: Apple® Secure Enclave, Google® Titan - Dedicated devices: Hardware Security Module -
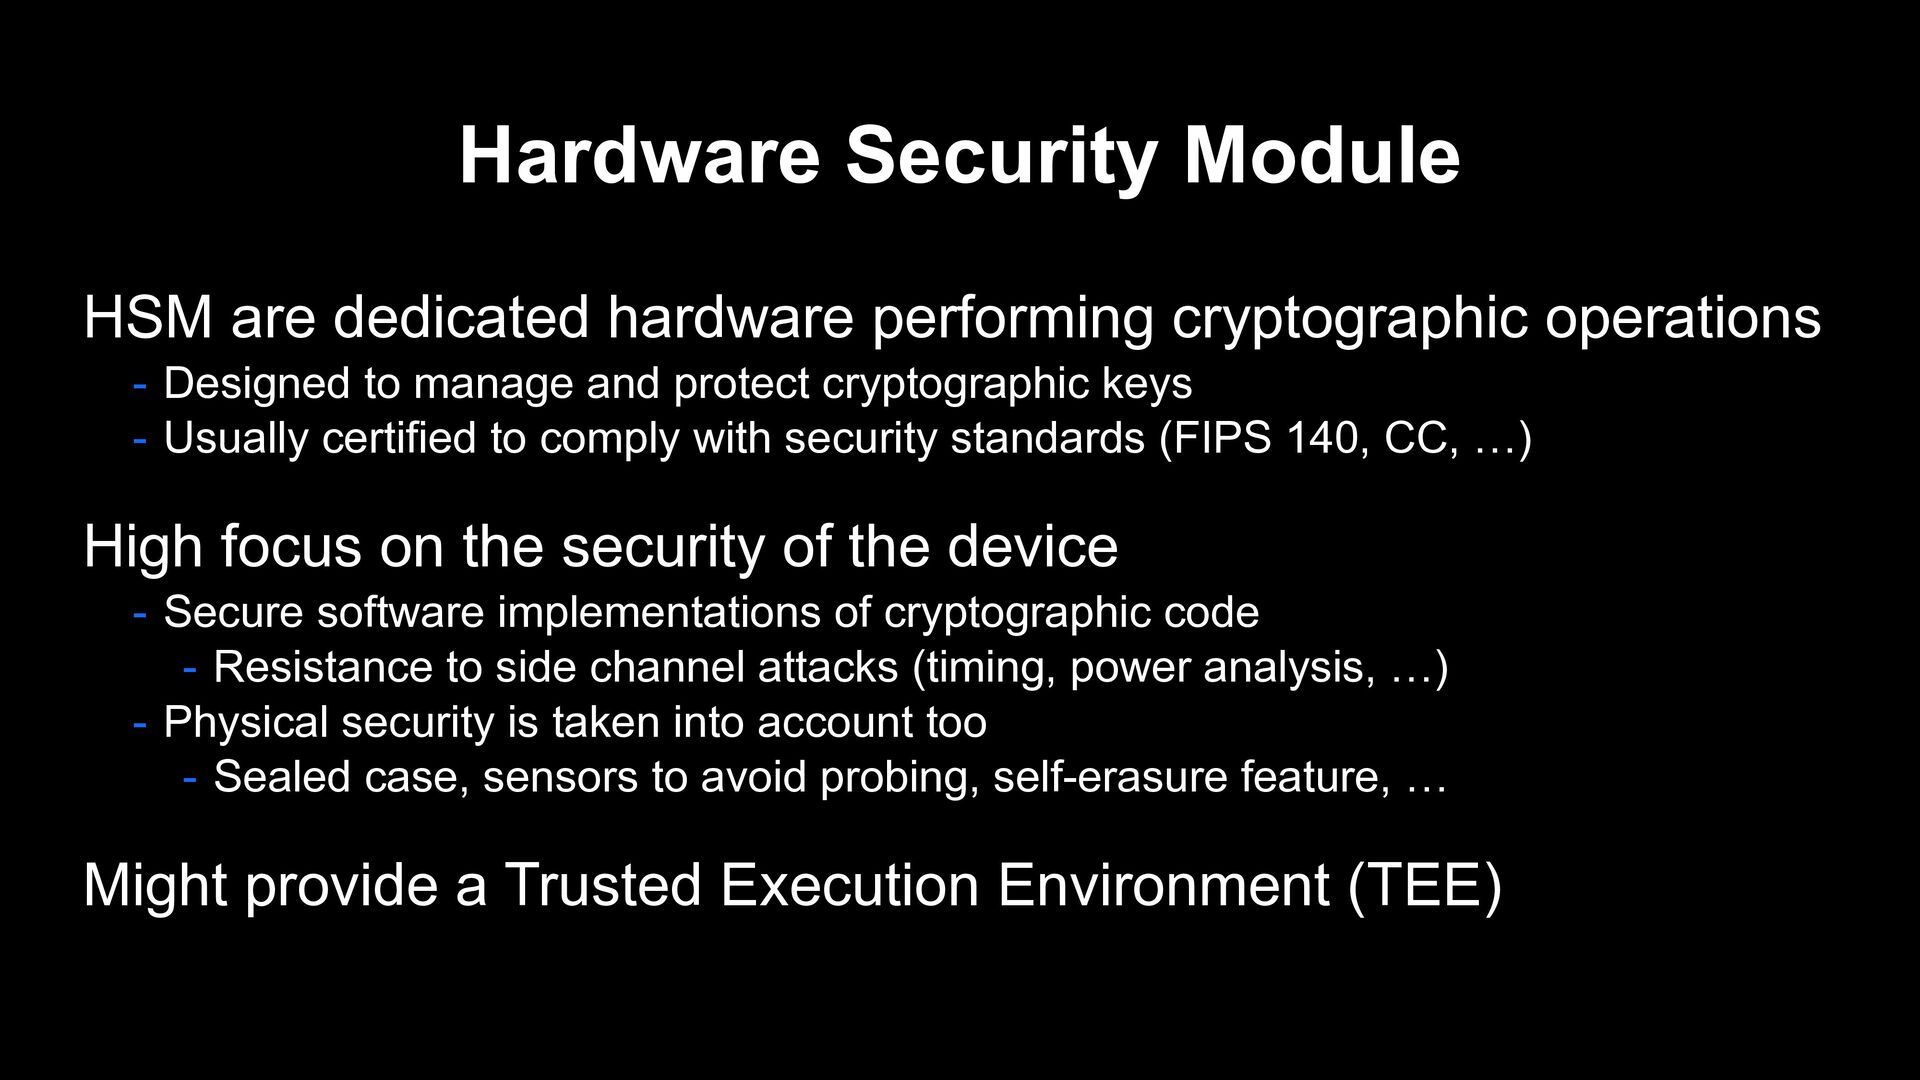
Hardware Security Module HSM are dedicated hardware performing cryptographic operations
- Designed to manage and protect cryptographic keys - Usually certified to comply with security standards (FIPS 140, CC, …) -
Hardware Security Module HSM are dedicated hardware performing cryptographic operations
- Designed to manage and protect cryptographic keys - Usually certified to comply with security standards (FIPS 140, CC, …) High focus on the security of the device - Secure software implementations of cryptographic code - Resistance to side channel attacks (timing, power analysis, …) - Physical security is taken into account too - Sealed case, sensors to avoid probing, self-erasure feature, … -
Hardware Security Module HSM are dedicated hardware performing cryptographic operations
- Designed to manage and protect cryptographic keys - Usually certified to comply with security standards (FIPS 140, CC, …) High focus on the security of the device - Secure software implementations of cryptographic code - Resistance to side channel attacks (timing, power analysis, …) - Physical security is taken into account too - Sealed case, sensors to avoid probing, self-erasure feature, … Might provide a Trusted Execution Environment (TEE) -
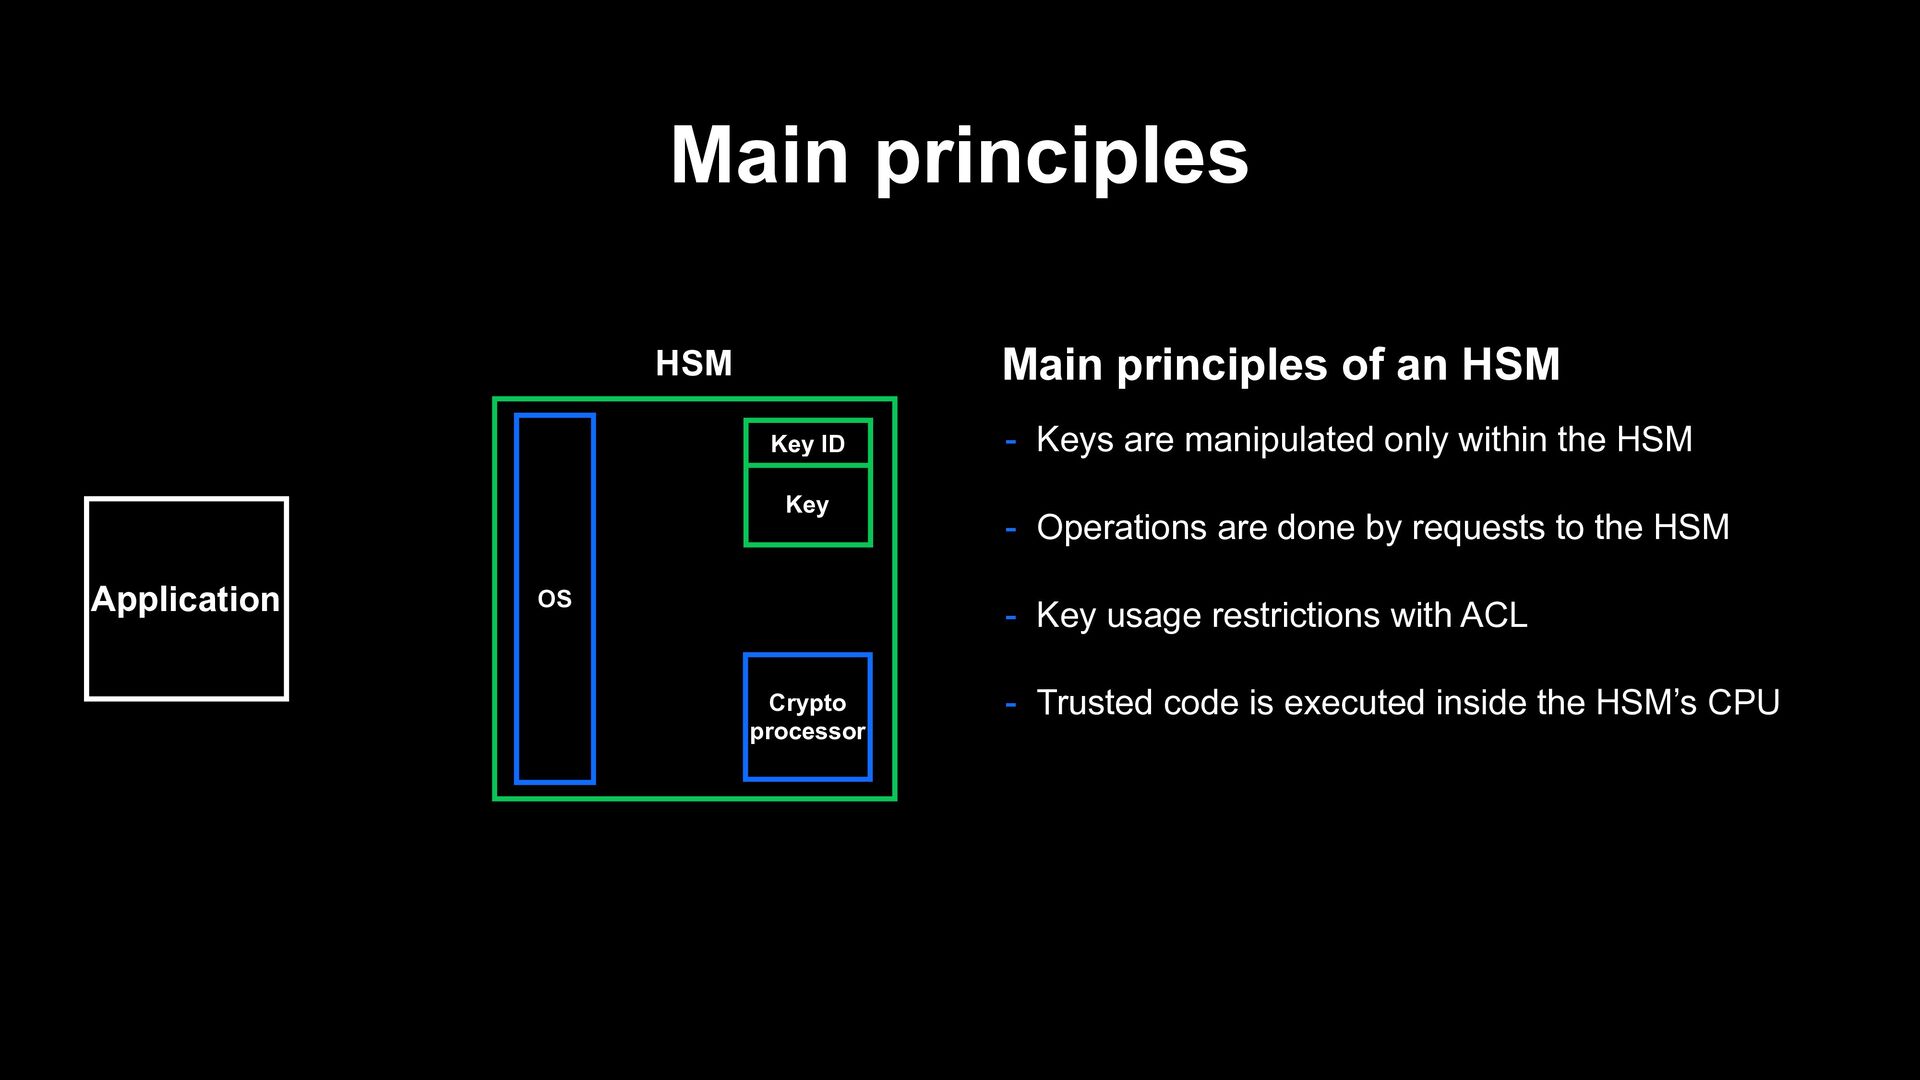
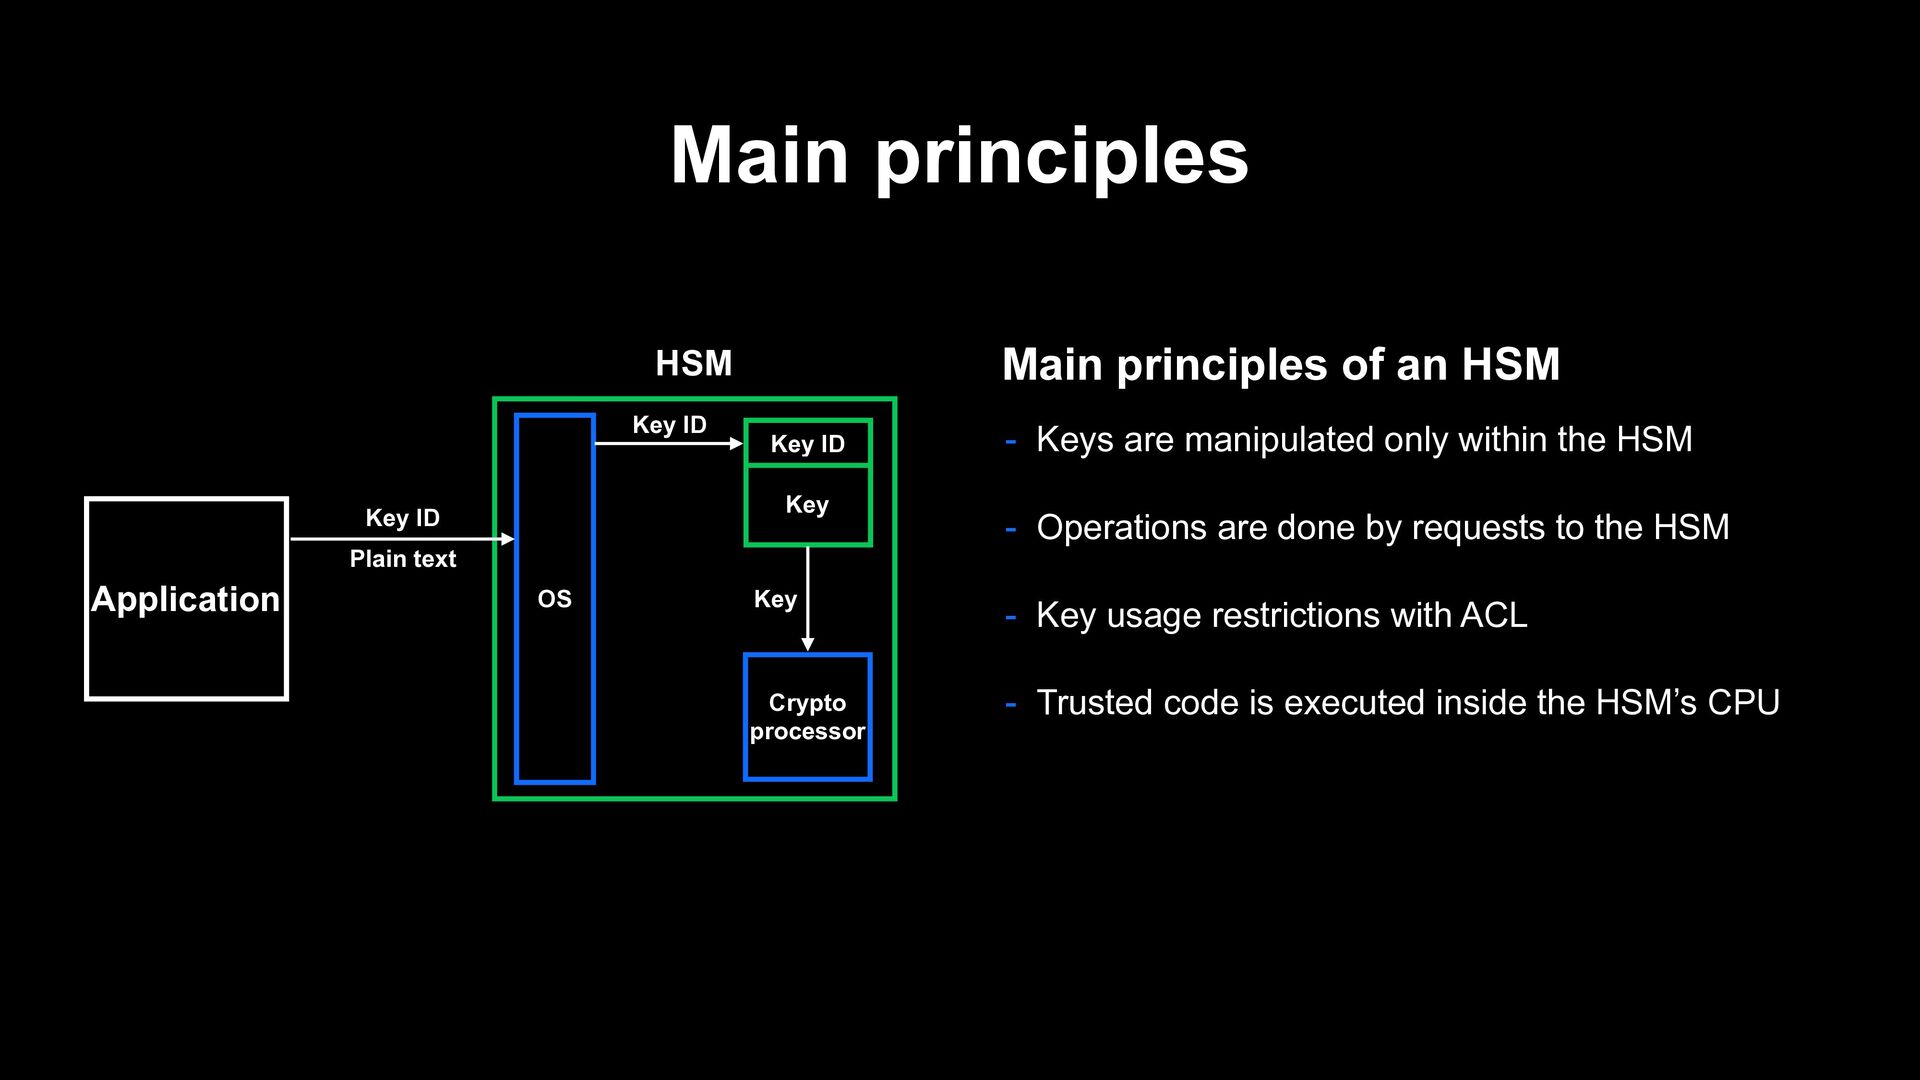
Main principles Main principles of an HSM - Keys are
manipulated only within the HSM - Operations are done by requests to the HSM - Key usage restrictions with ACL - Trusted code is executed inside the HSM’s CPU HSM OS Crypto processor Application Key Key ID -
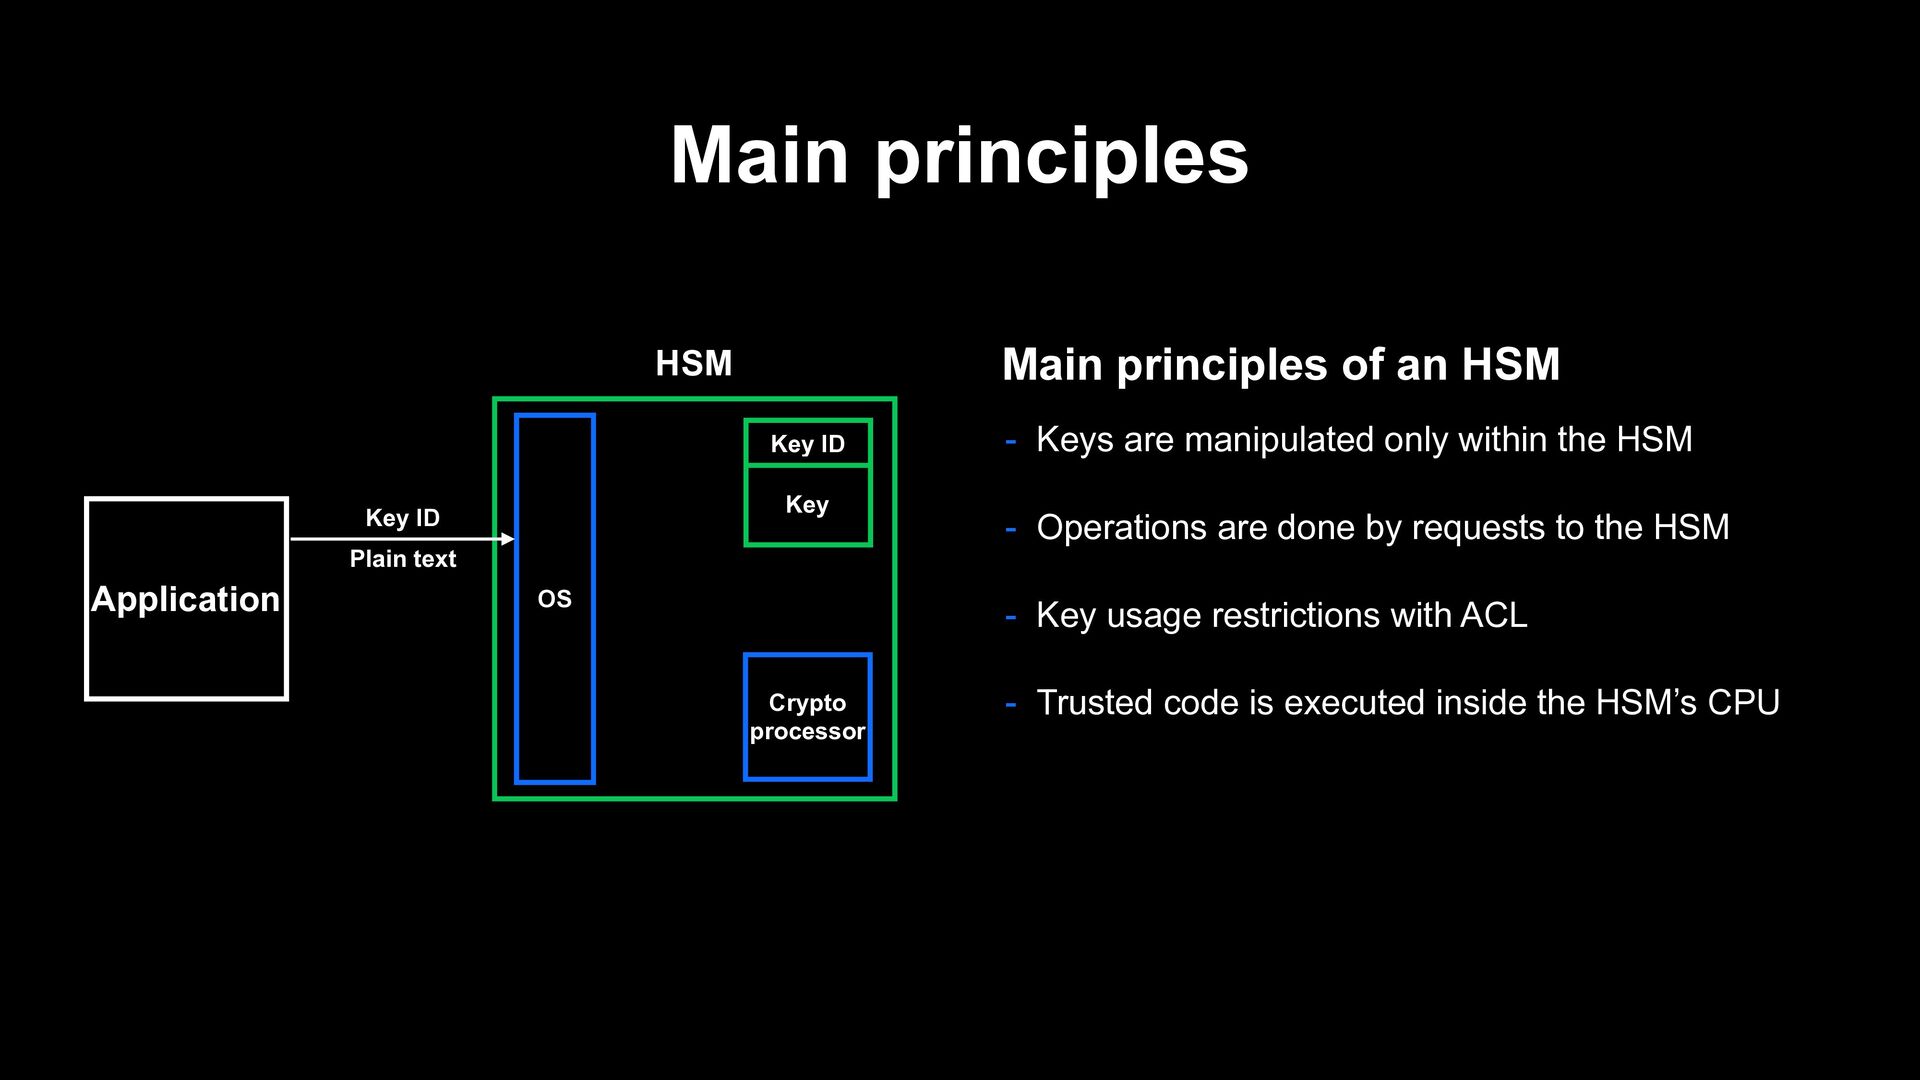
Main principles Main principles of an HSM - Keys are
manipulated only within the HSM - Operations are done by requests to the HSM - Key usage restrictions with ACL - Trusted code is executed inside the HSM’s CPU HSM OS Crypto processor Application Key Key ID Key ID Plain text -
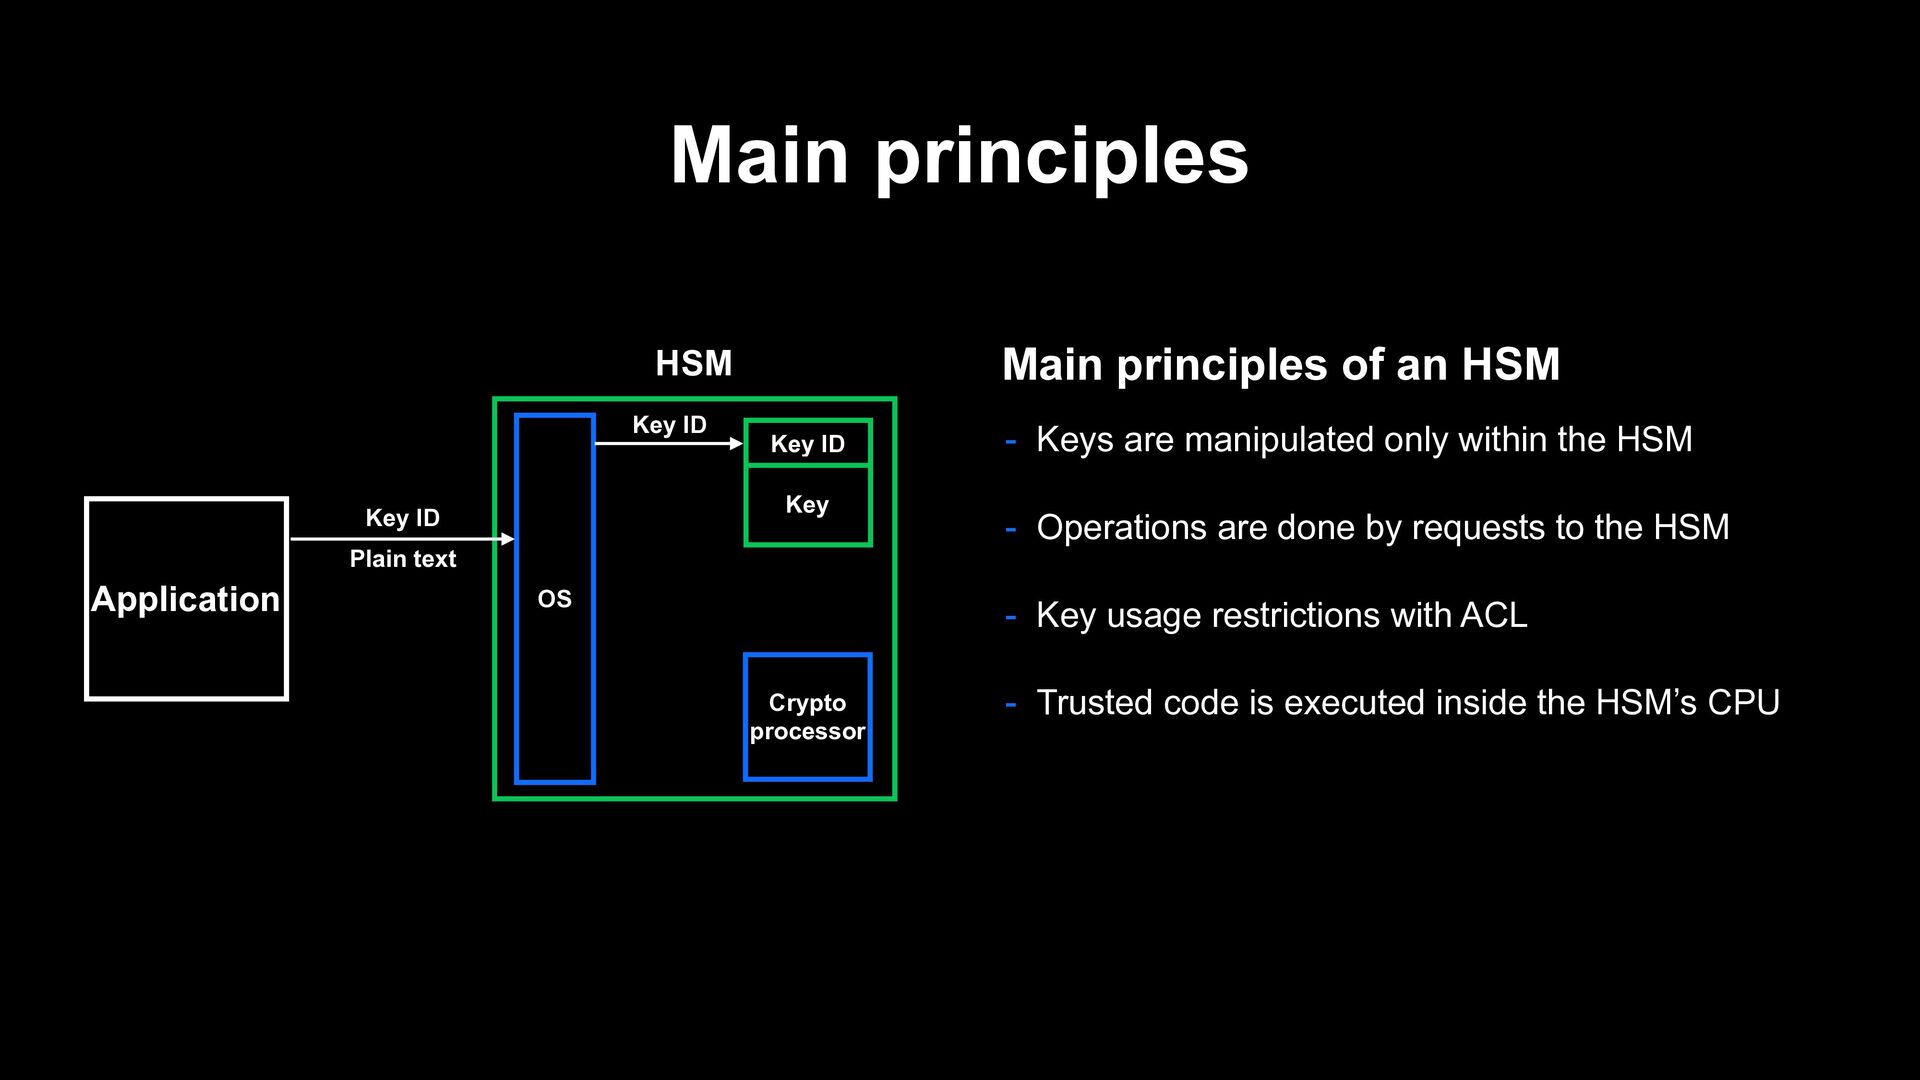
Main principles Main principles of an HSM - Keys are
manipulated only within the HSM - Operations are done by requests to the HSM - Key usage restrictions with ACL - Trusted code is executed inside the HSM’s CPU HSM OS Crypto processor Application Key Key ID Key ID Plain text Key ID -
Main principles Main principles of an HSM - Keys are
manipulated only within the HSM - Operations are done by requests to the HSM - Key usage restrictions with ACL - Trusted code is executed inside the HSM’s CPU HSM OS Crypto processor Application Key Key ID Key ID Plain text Key ID Key -
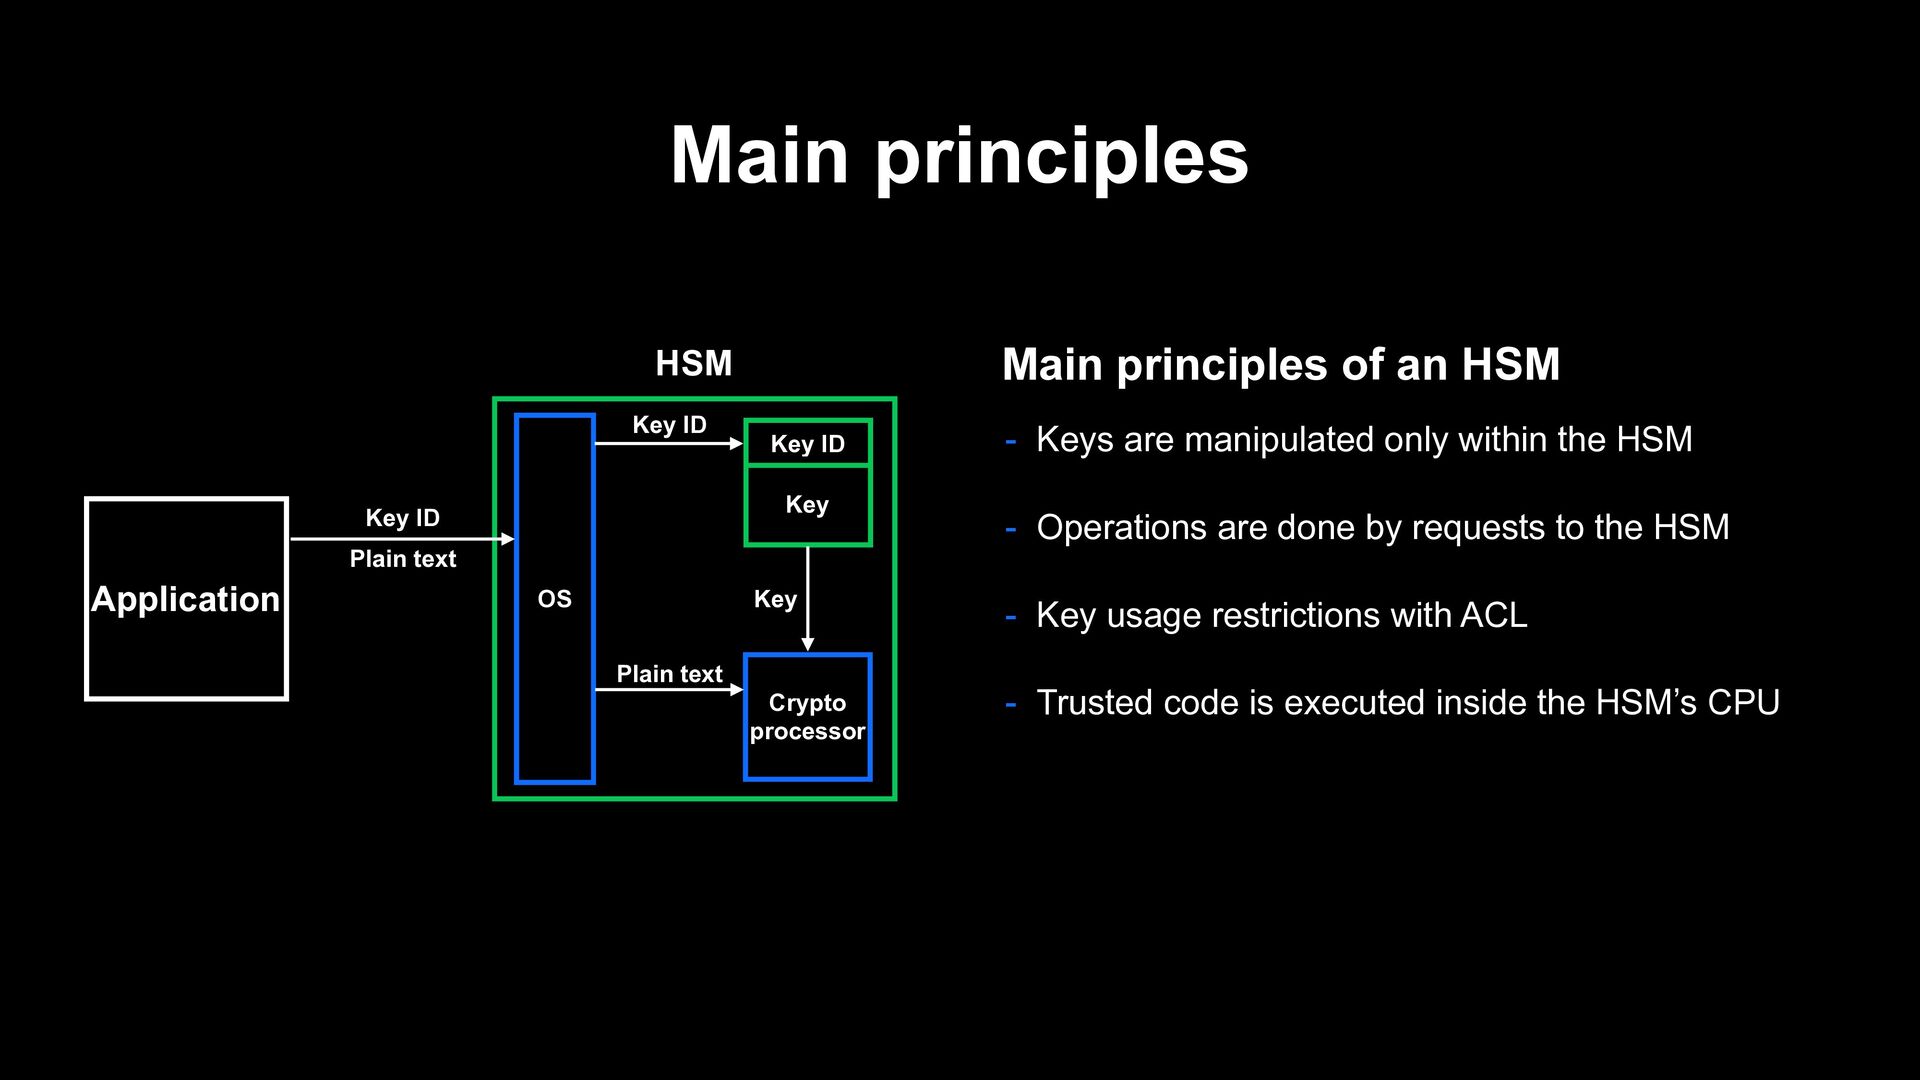
Main principles Main principles of an HSM - Keys are
manipulated only within the HSM - Operations are done by requests to the HSM - Key usage restrictions with ACL - Trusted code is executed inside the HSM’s CPU HSM OS Crypto processor Application Key Key ID Key ID Plain text Key ID Plain text Key -
Main principles Main principles of an HSM - Keys are
manipulated only within the HSM - Operations are done by requests to the HSM - Key usage restrictions with ACL - Trusted code is executed inside the HSM’s CPU HSM OS Crypto processor Application Key Key ID Key ID Plain text Key ID Plain text Cipher text Key -
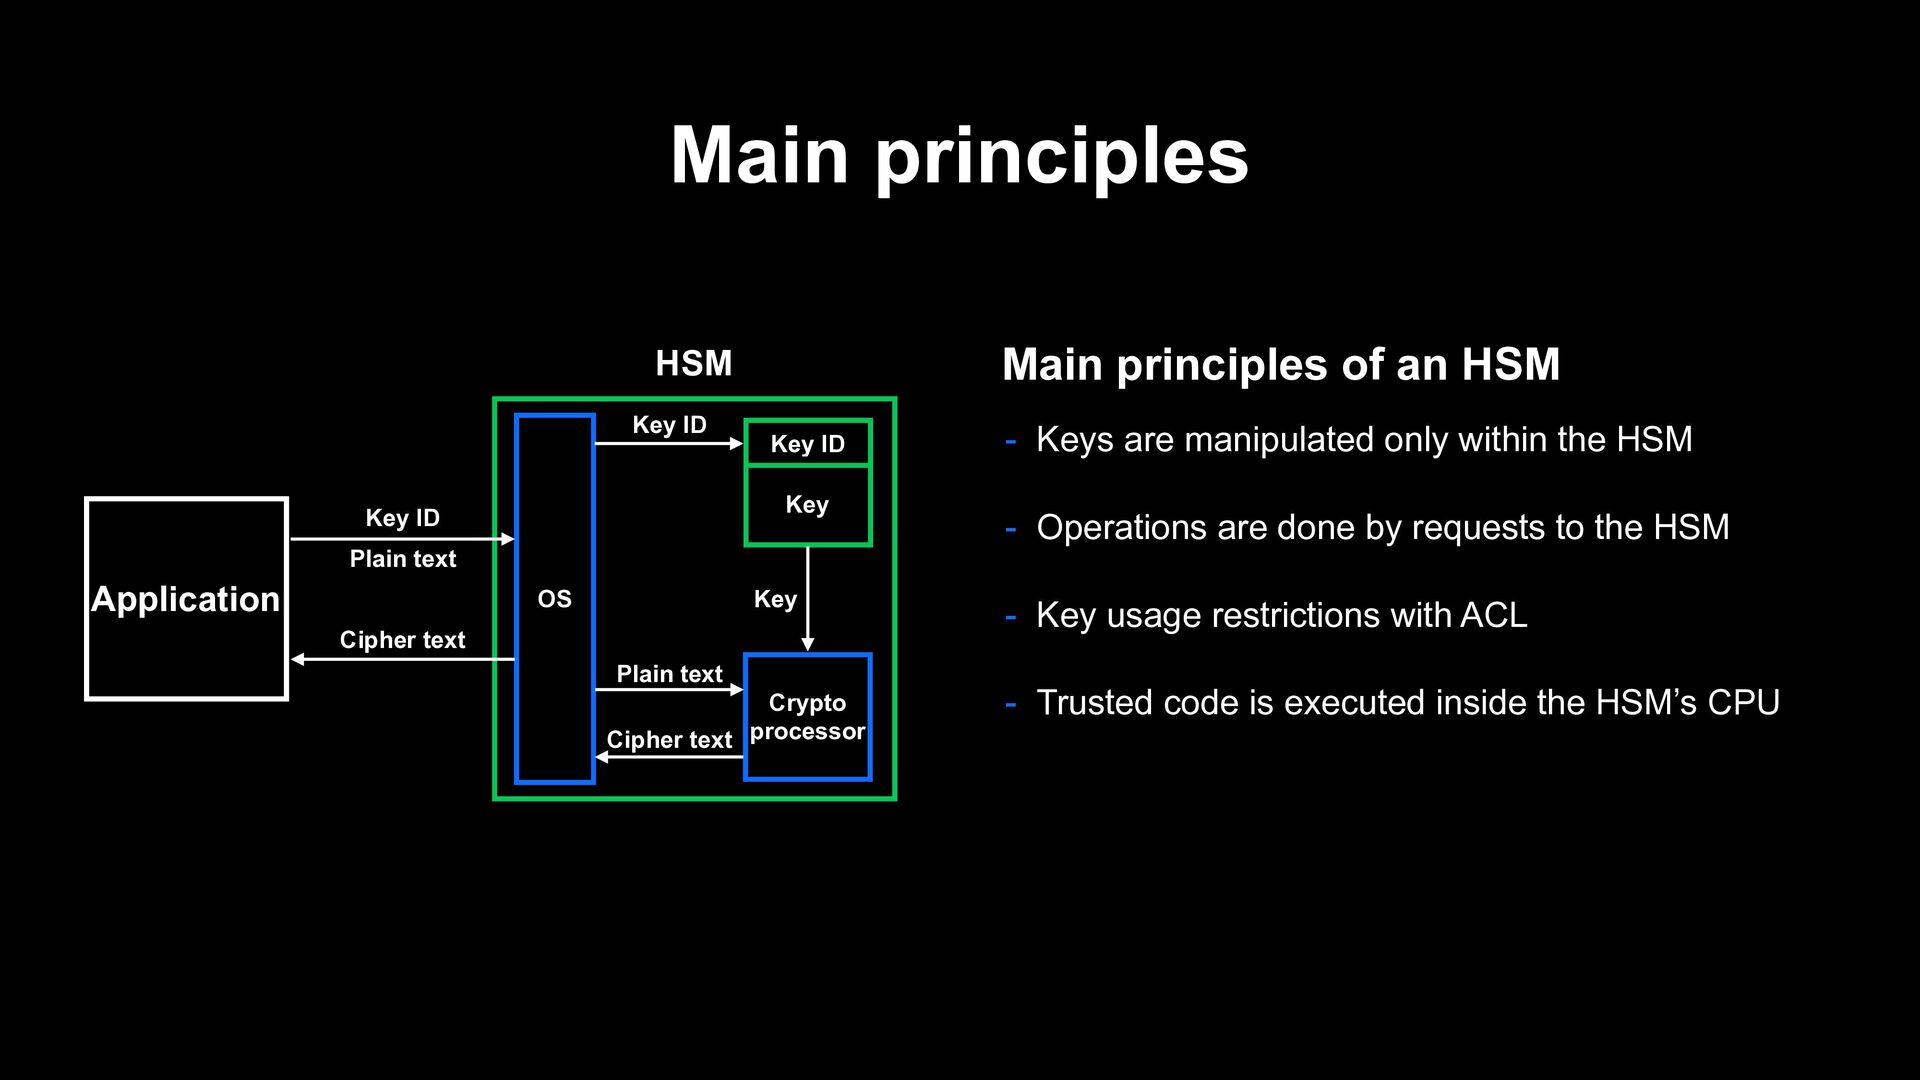
Main principles Main principles of an HSM - Keys are
manipulated only within the HSM - Operations are done by requests to the HSM - Key usage restrictions with ACL - Trusted code is executed inside the HSM’s CPU HSM OS Crypto processor Application Key Key ID Cipher text Key ID Plain text Key ID Plain text Cipher text Key -
Operational Costs of HSM Development complexity - Unusual development environment
(CPU architecture, OS, …) - Suboptimal performances for general purpose computing -
Operational Costs of HSM Development complexity - Unusual development environment
(CPU architecture, OS, …) - Suboptimal performances for general purpose computing High availability and high performance required - Unit price of an HSM is high - Spare units needed quickly in case of hardware failures -
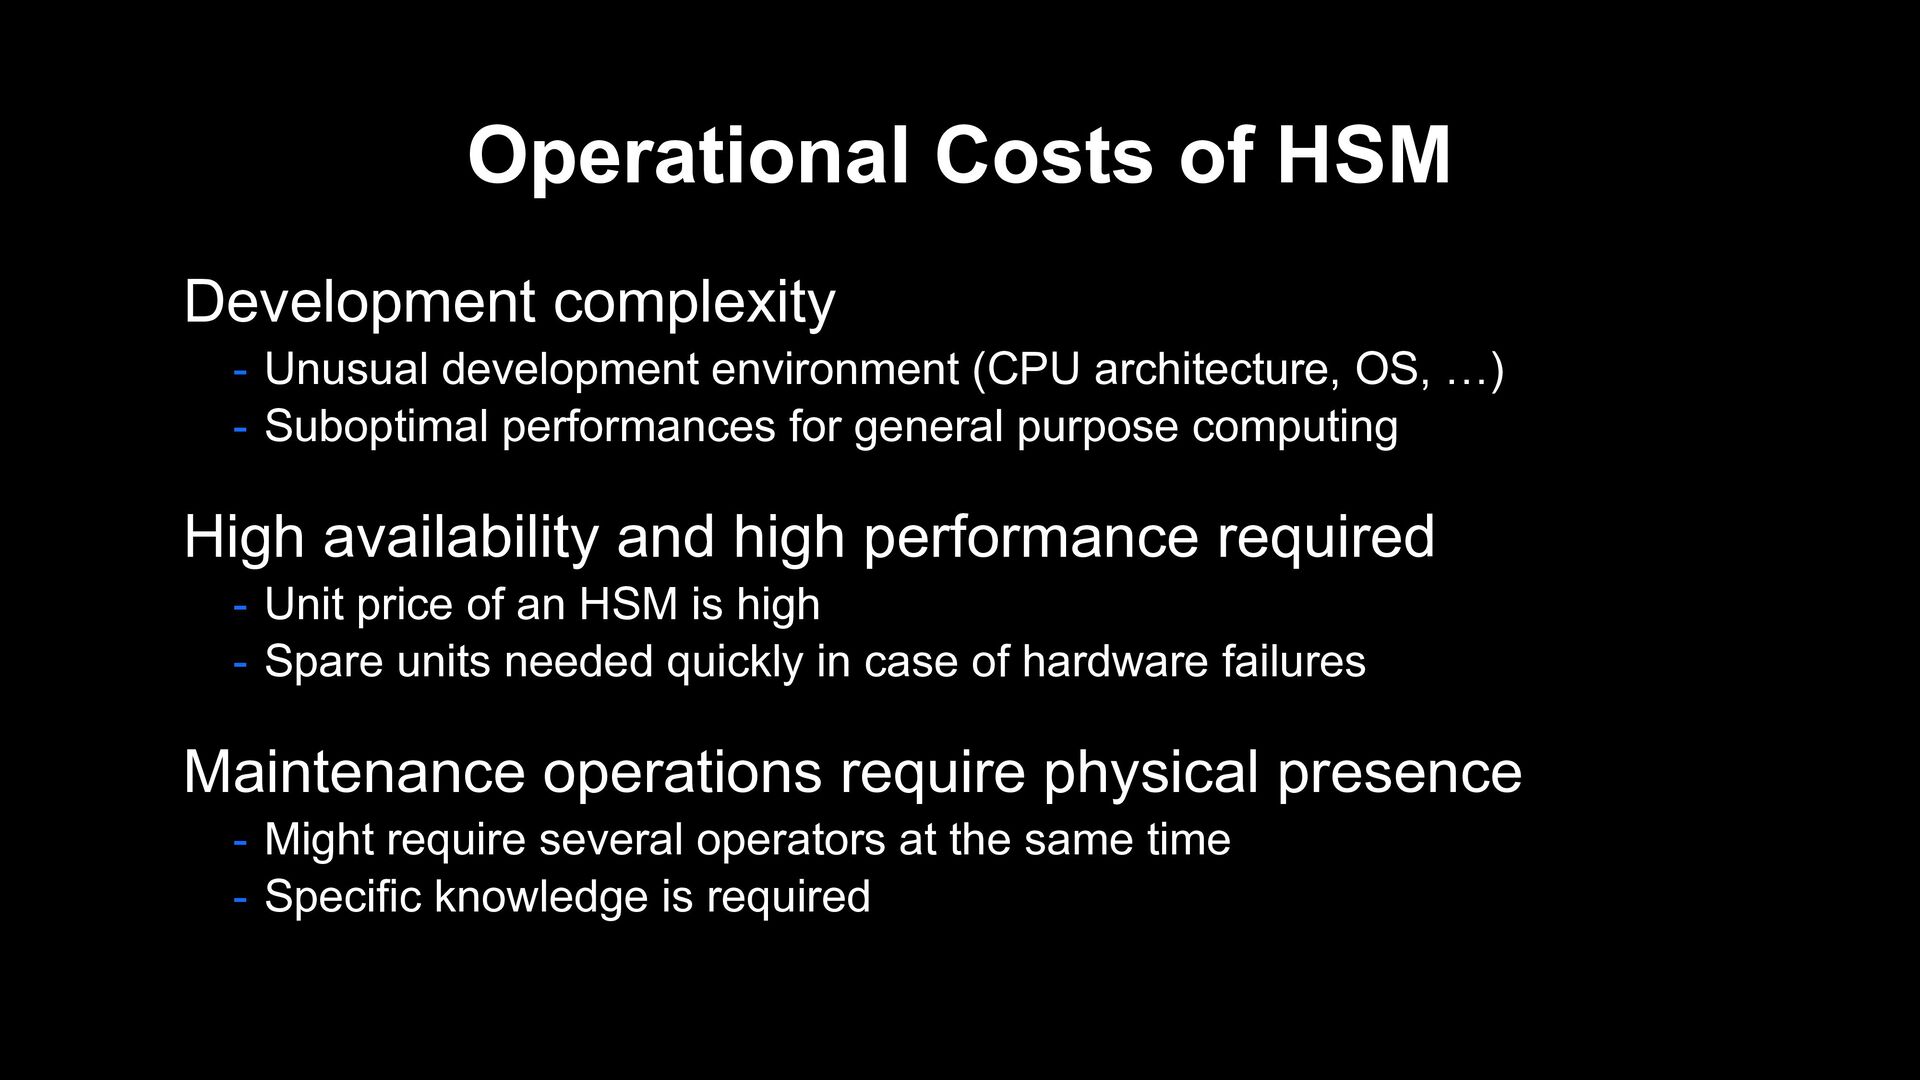
Operational Costs of HSM Development complexity - Unusual development environment
(CPU architecture, OS, …) - Suboptimal performances for general purpose computing High availability and high performance required - Unit price of an HSM is high - Spare units needed quickly in case of hardware failures Maintenance operations require physical presence - Might require several operators at the same time - Specific knowledge is required -
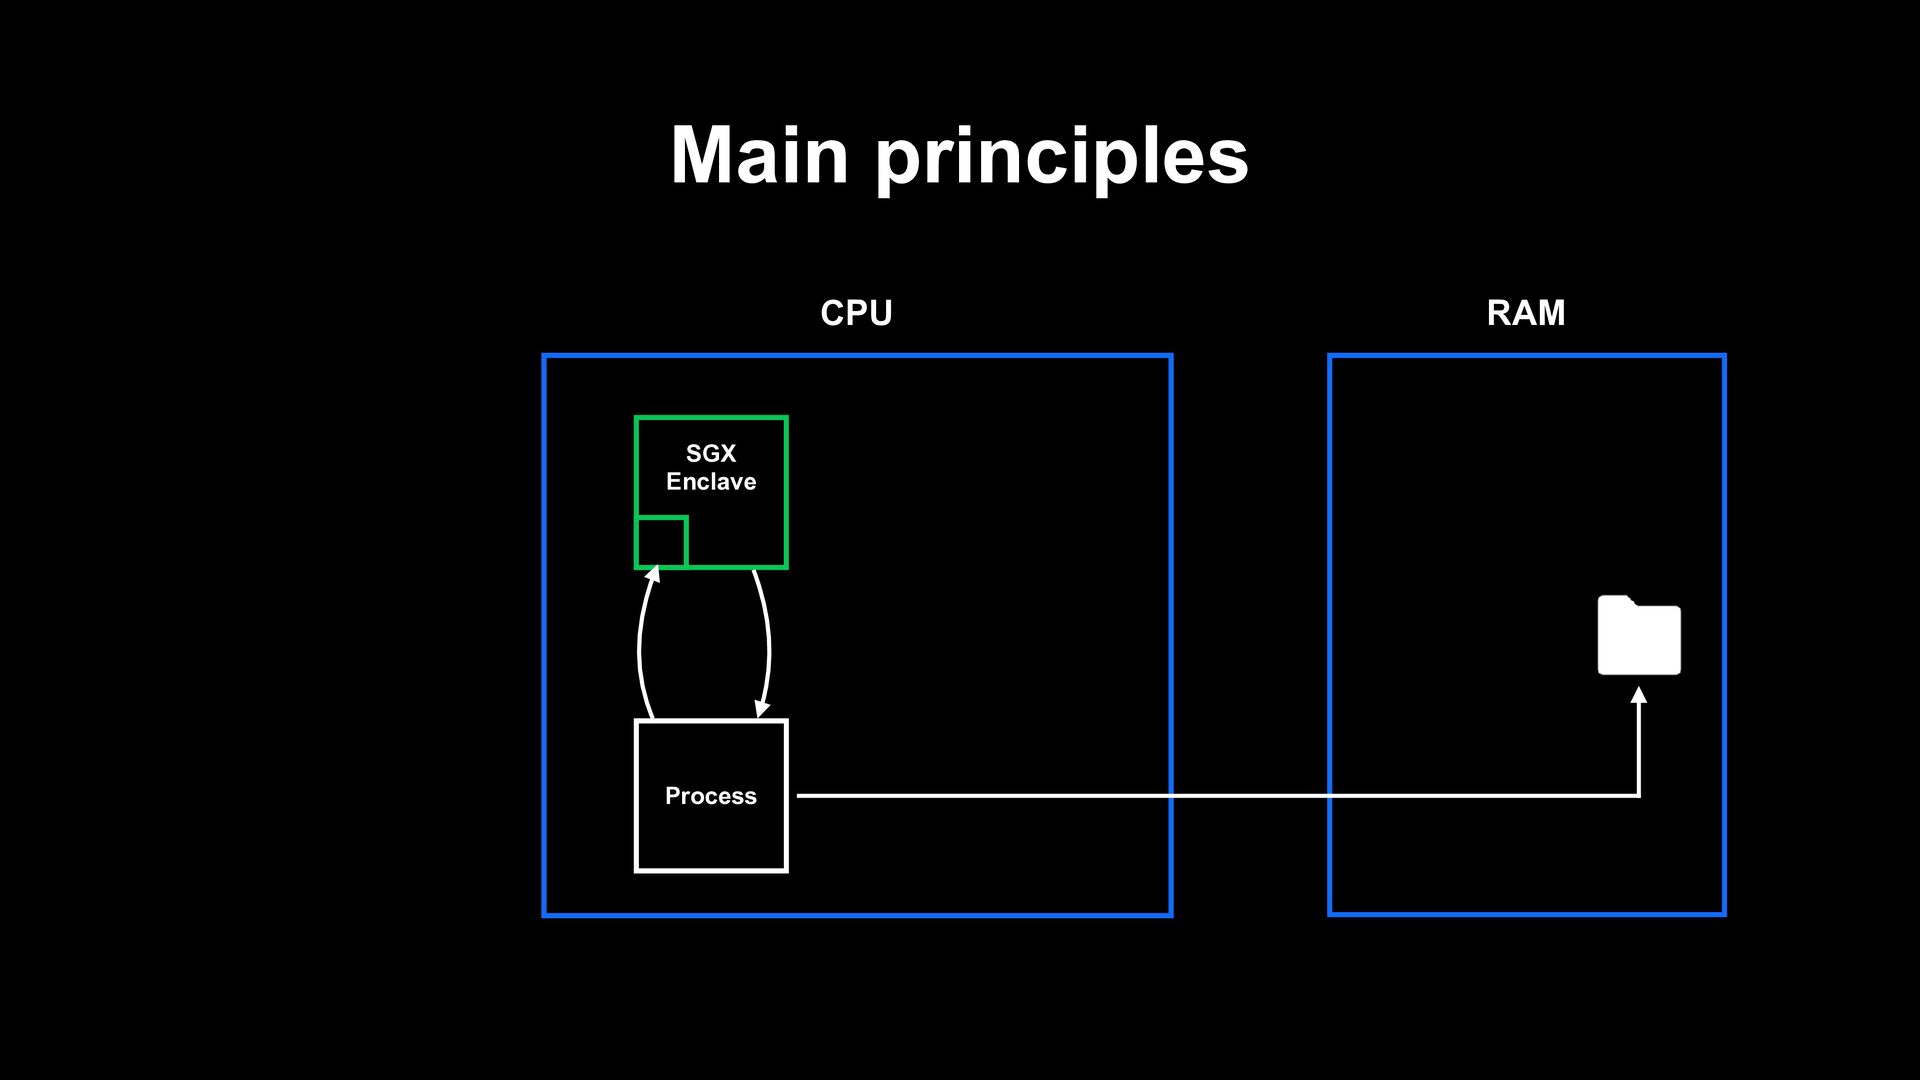
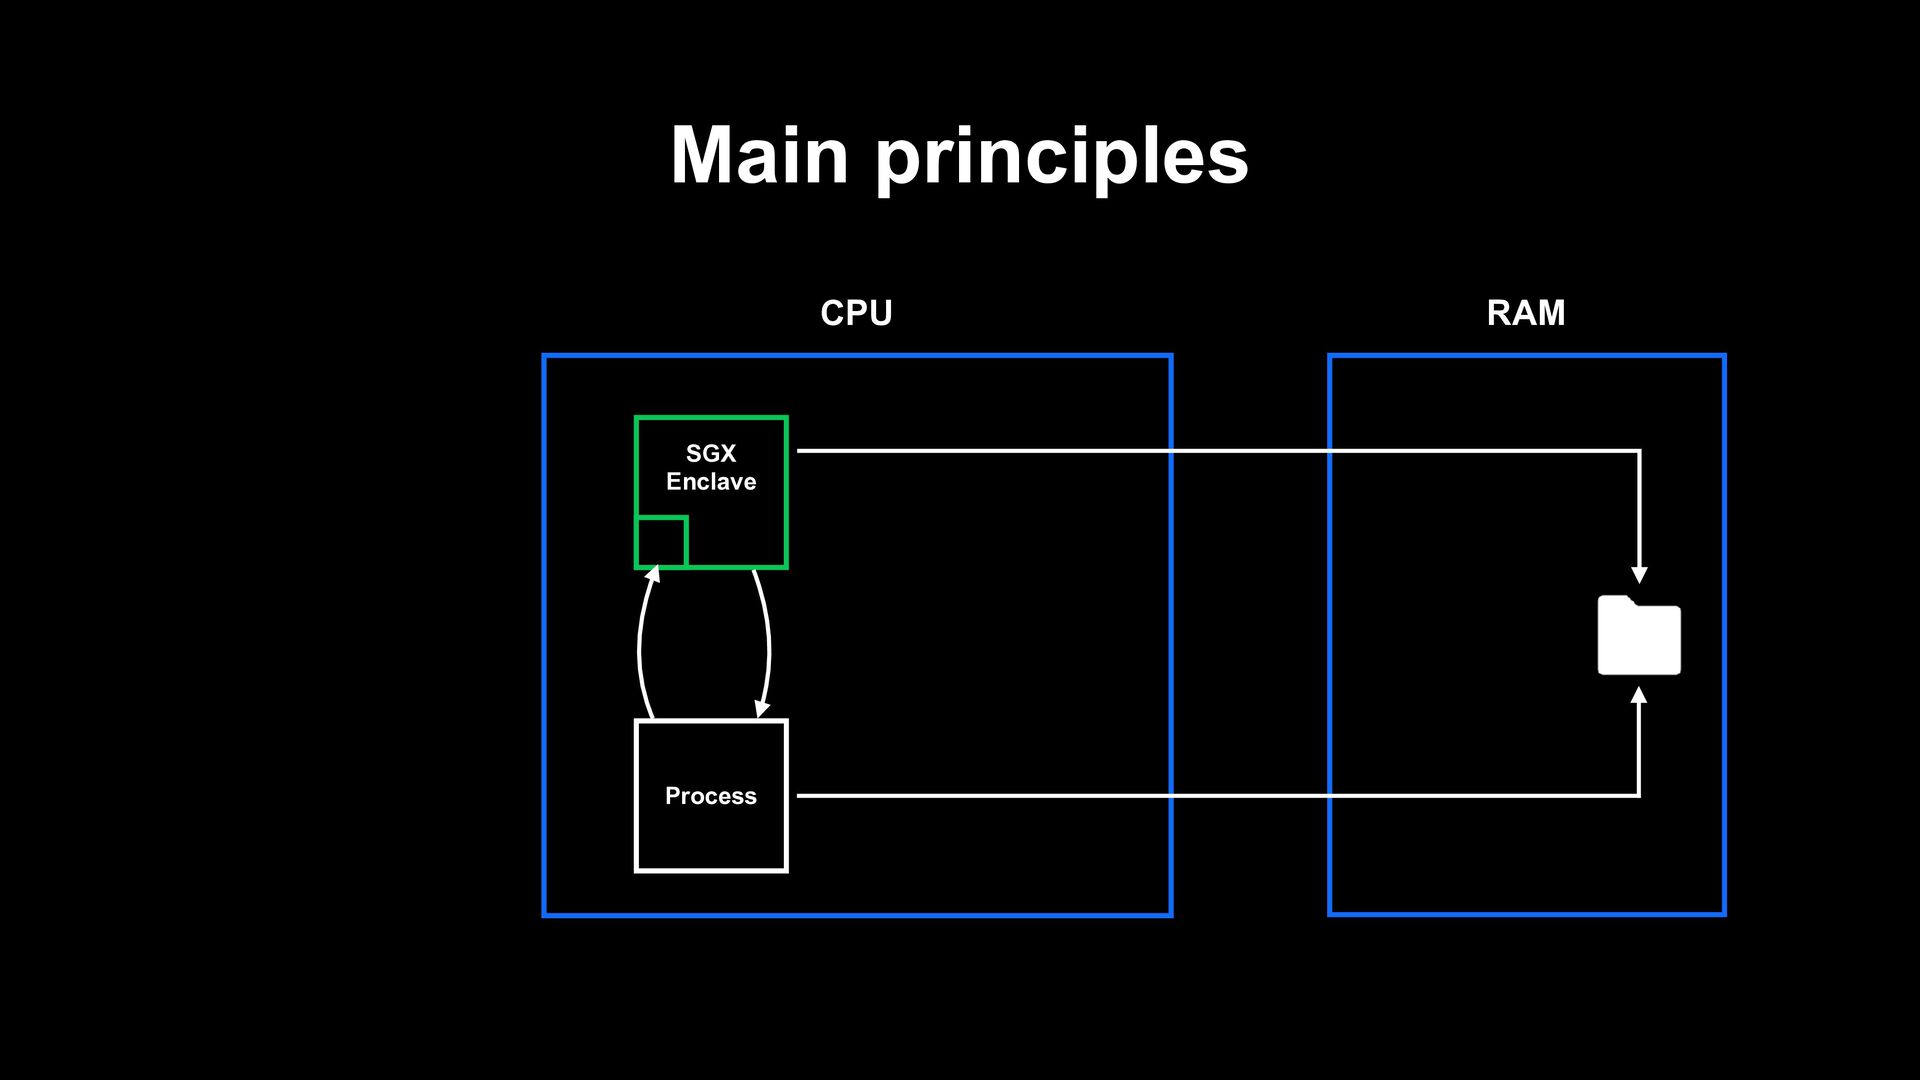
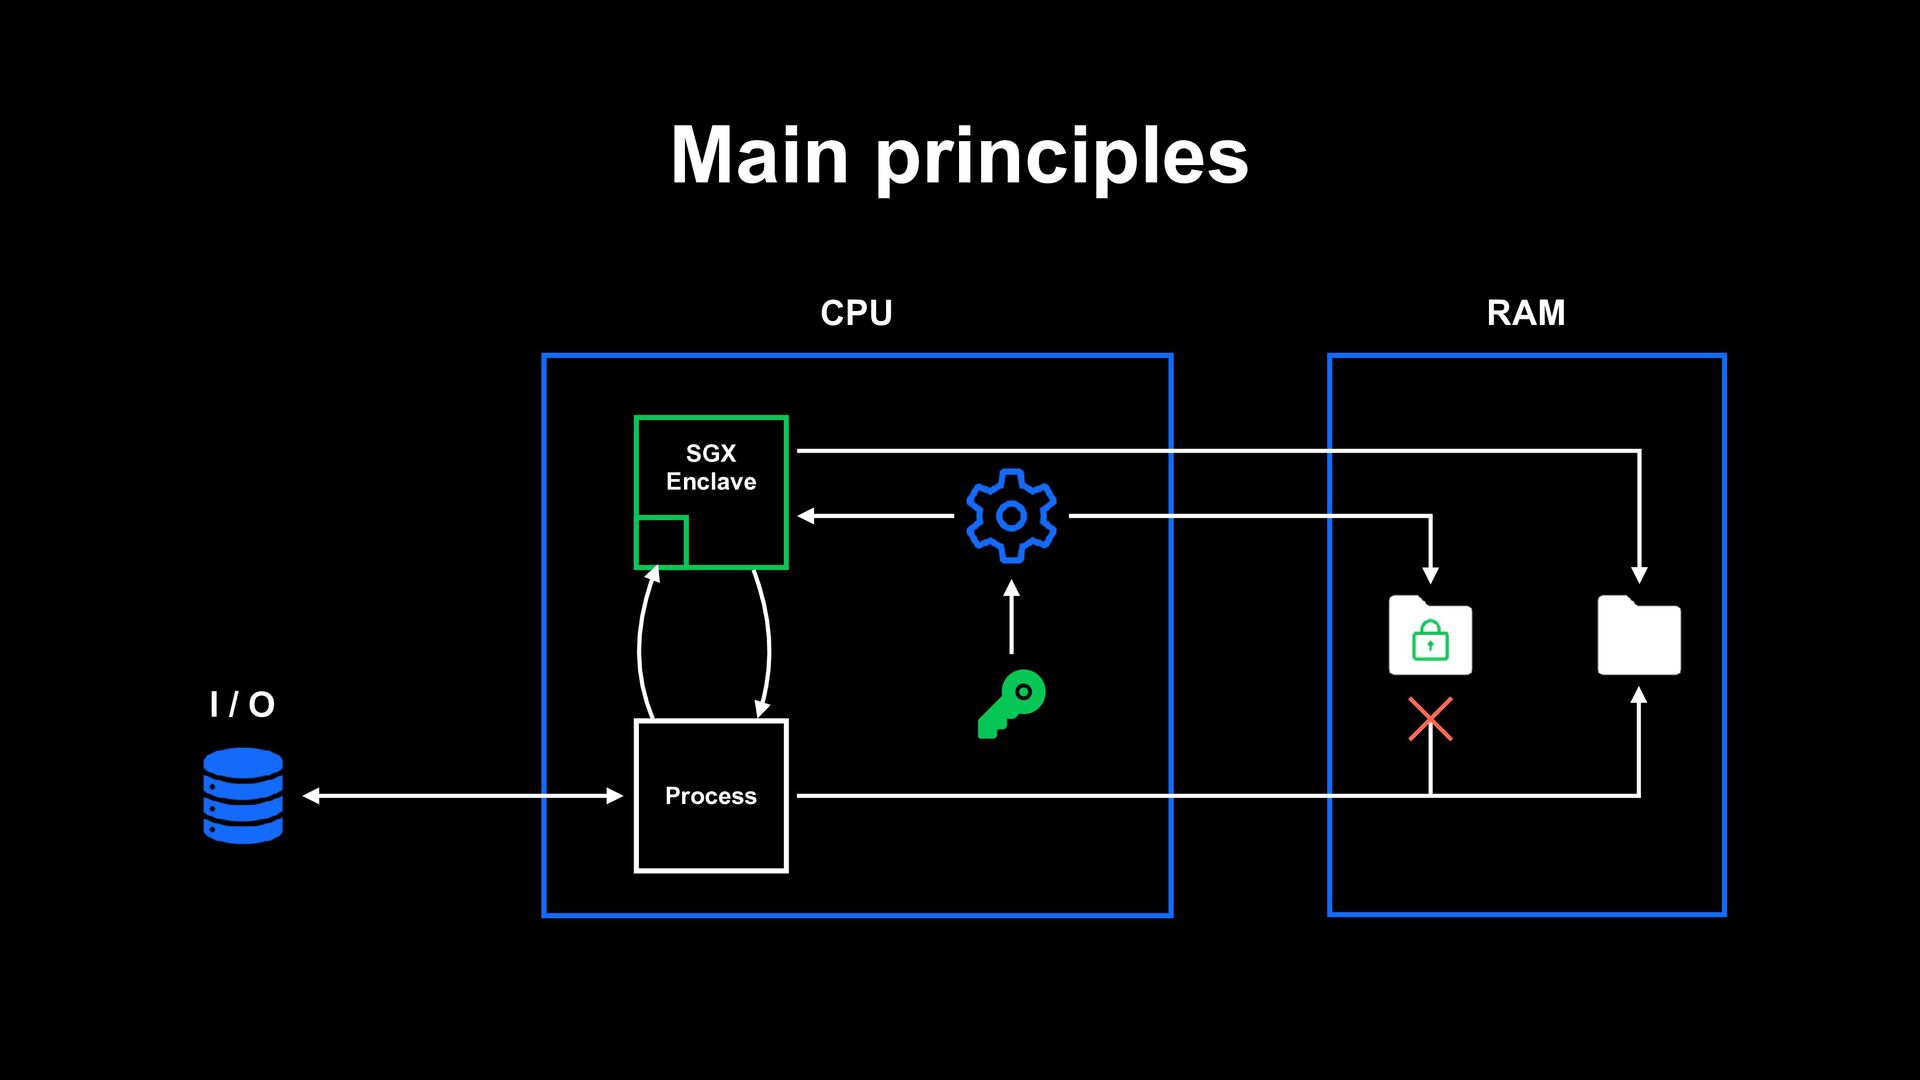
Intel® Software Guard Extensions What is Intel® SGX - Intel®
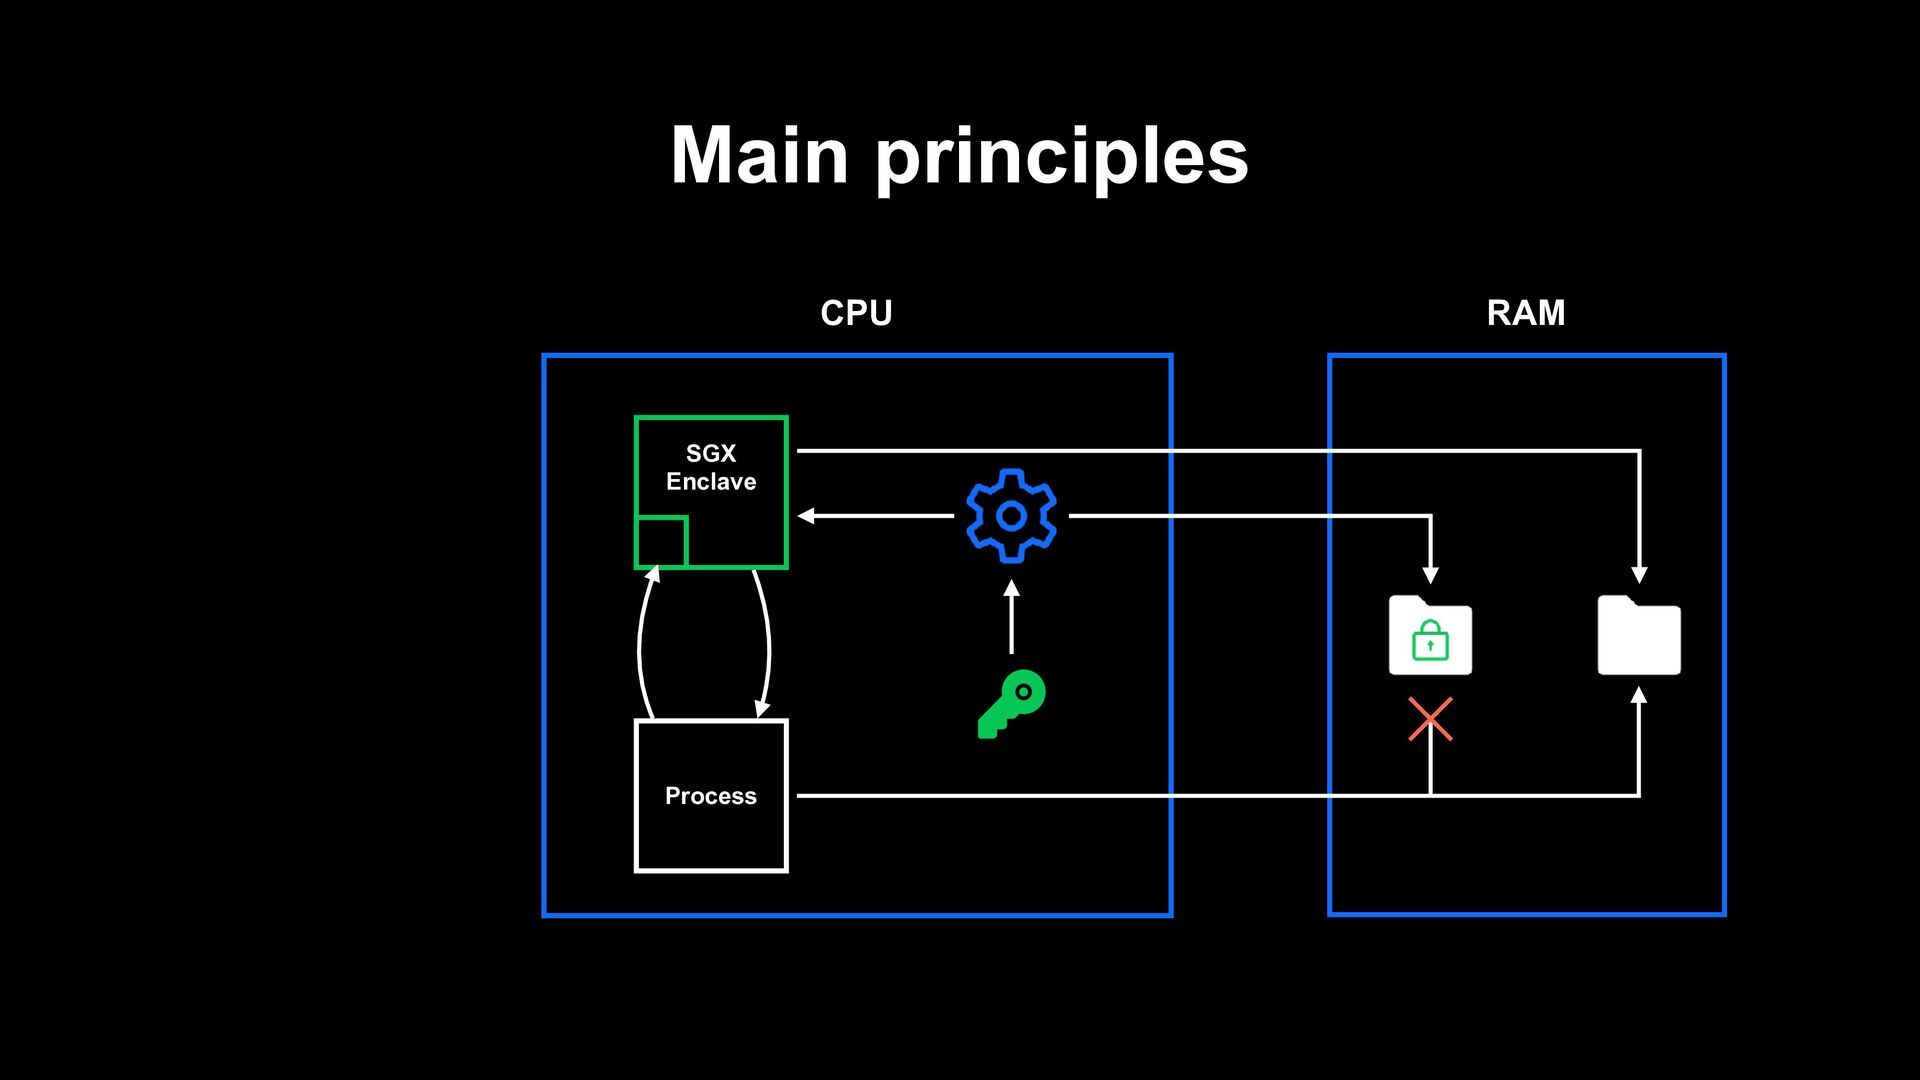
proposal for Trusted Computing directly in the CPU - Implemented as 18 new assembly instructions - Security critical code is signed and isolated in an enclave - Enclaves are totally isolated from other processes -
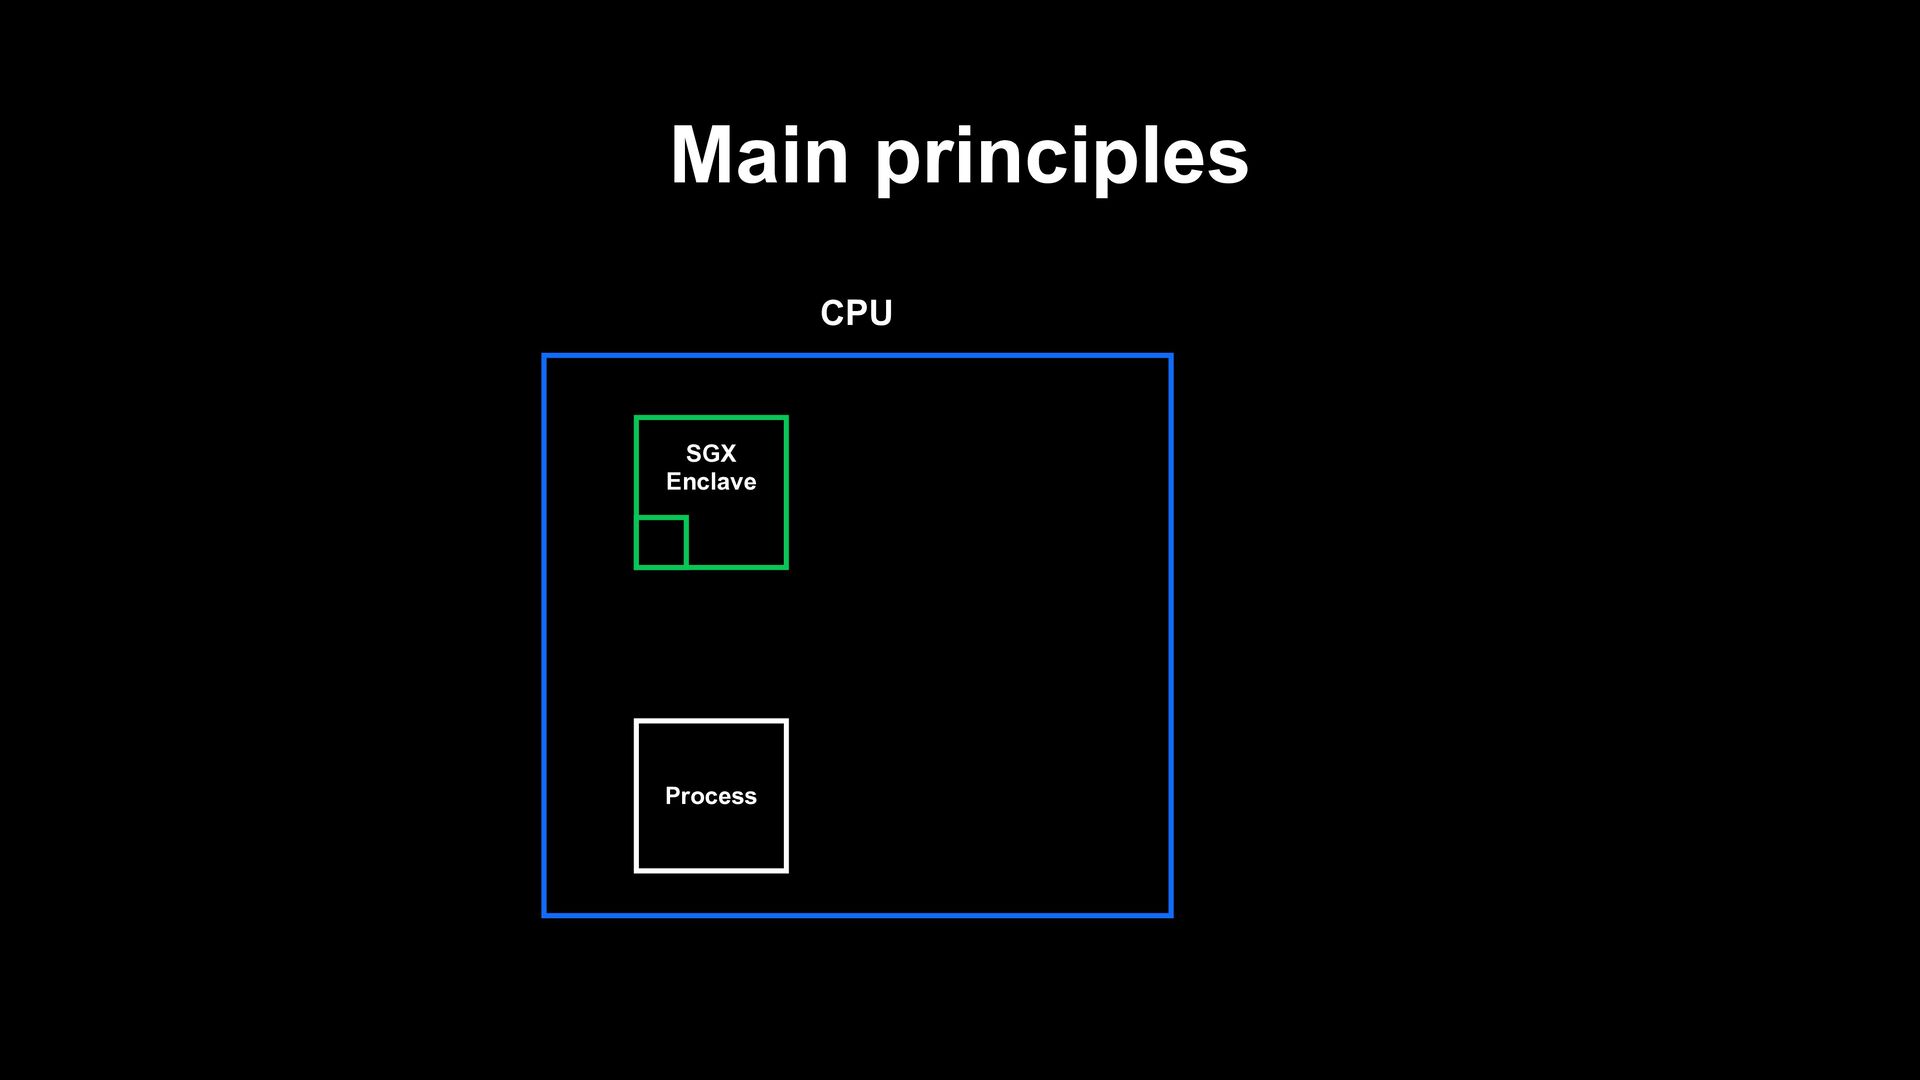
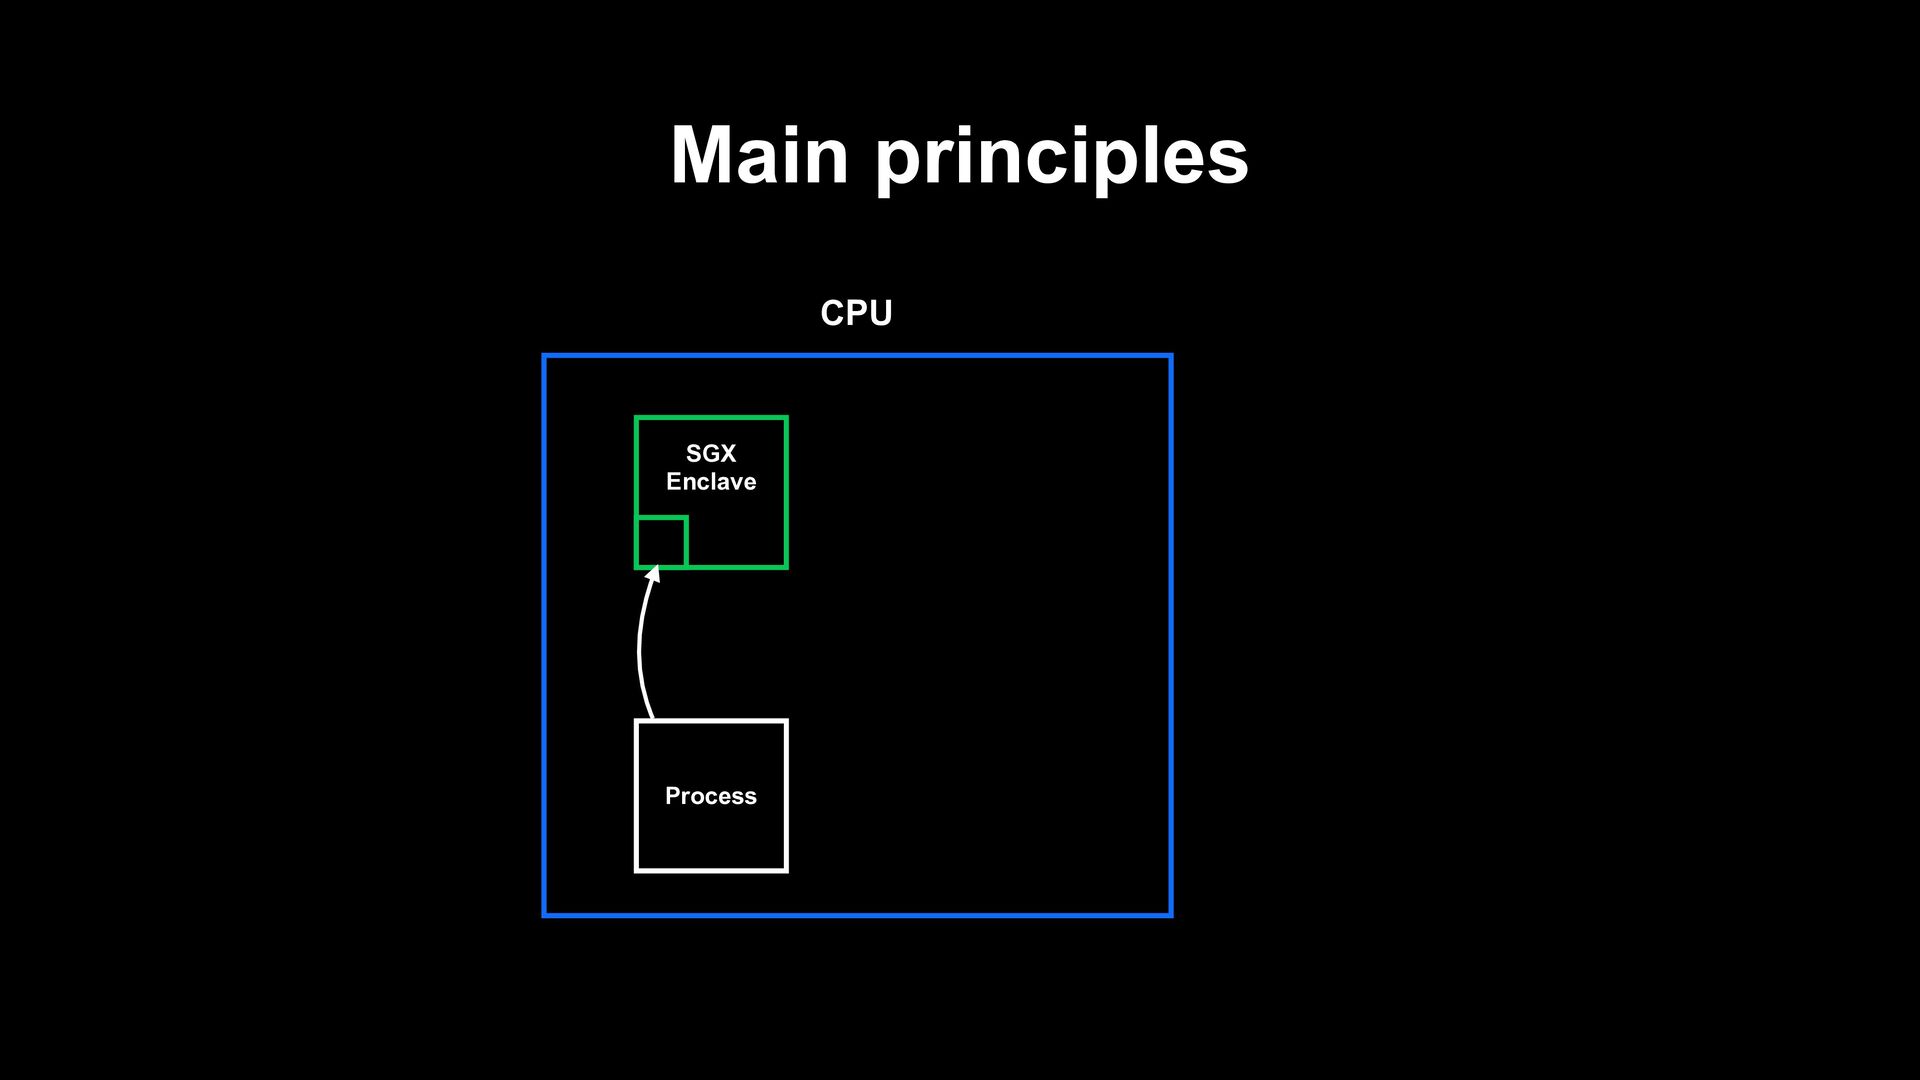
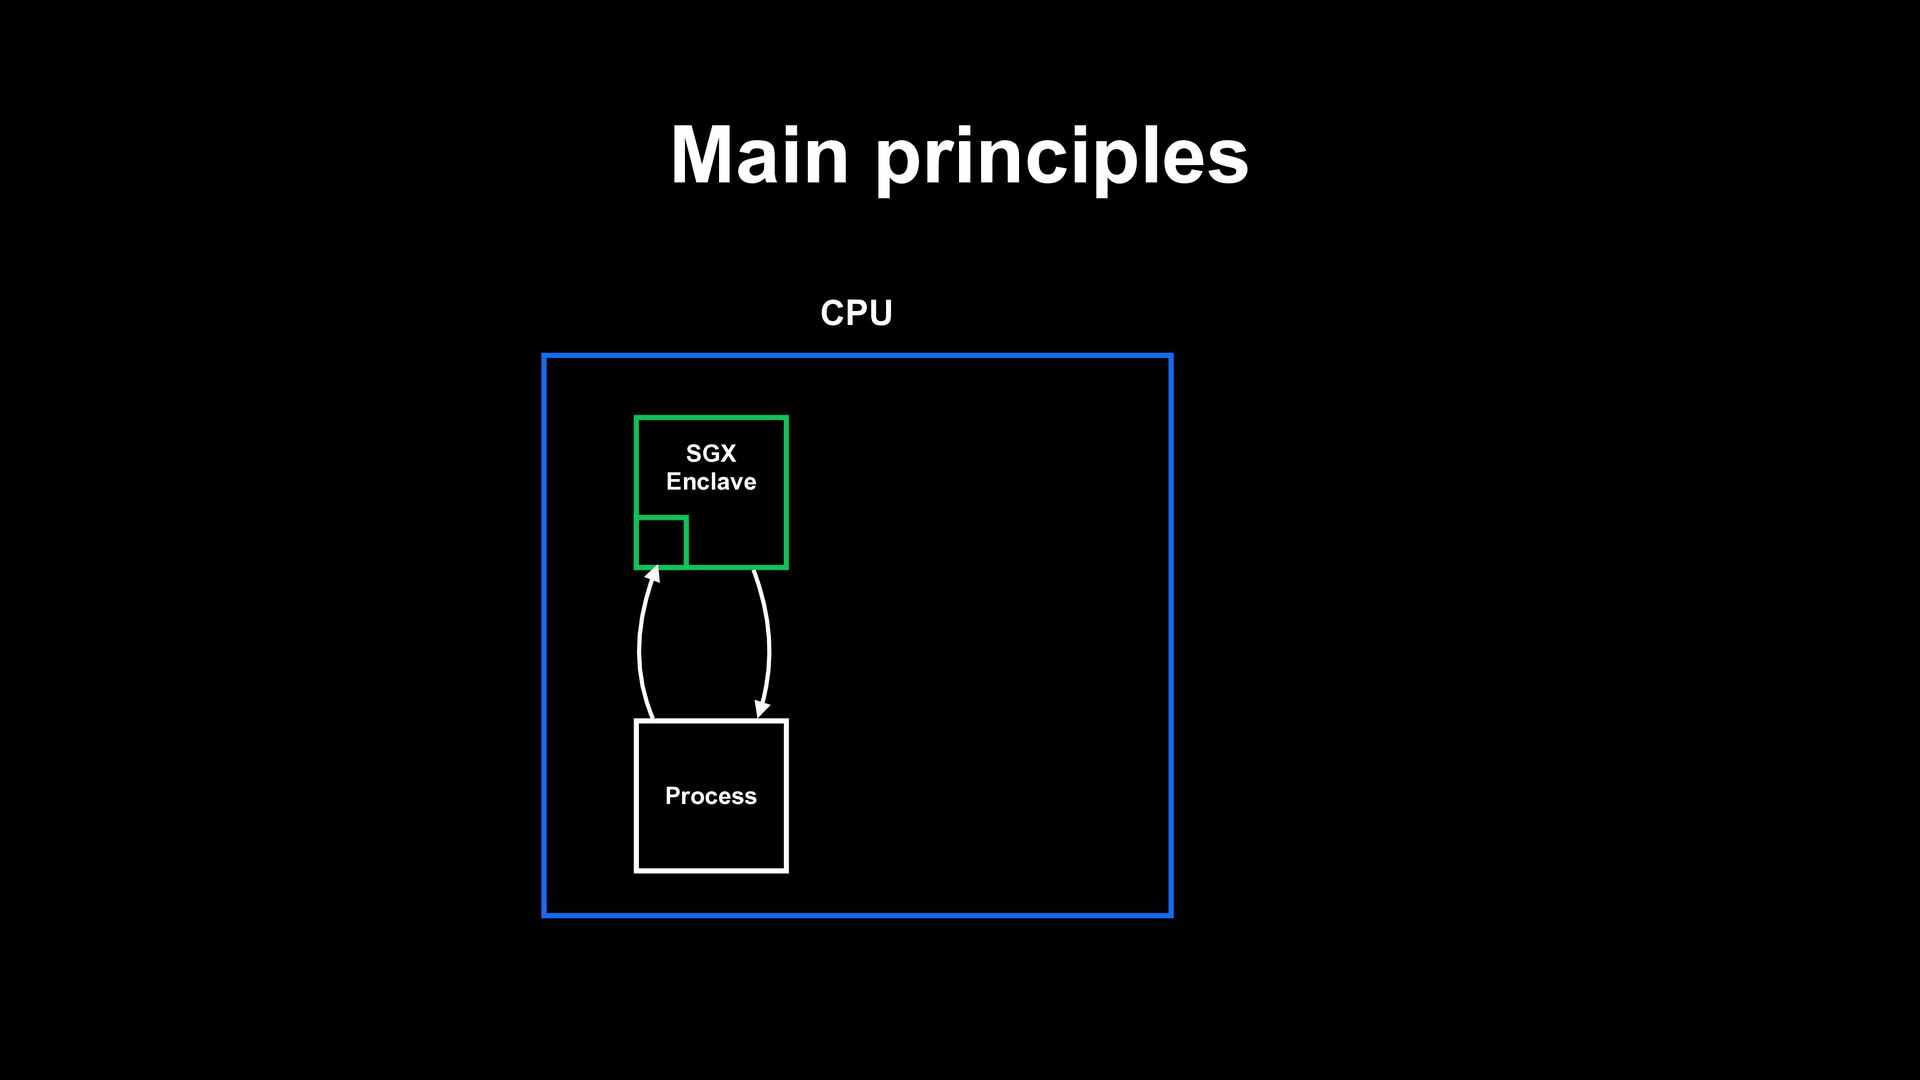
Main principles Intel® SGX Developer Guide defines 3 objectives to
have trusted computing: - Measurement: instantiation of the code in a trusted environment - Sealing: safe export of secret from the trusted environment - Attestation: provability that the code is running in a trusted environment -
Measurement of code Instantiation of the code in a trusted
environment - Enclaves are signed at compilation time - Signature is verified when the enclave is loaded by the CPU - Enclave code can only be accessed at well-defined entry points -
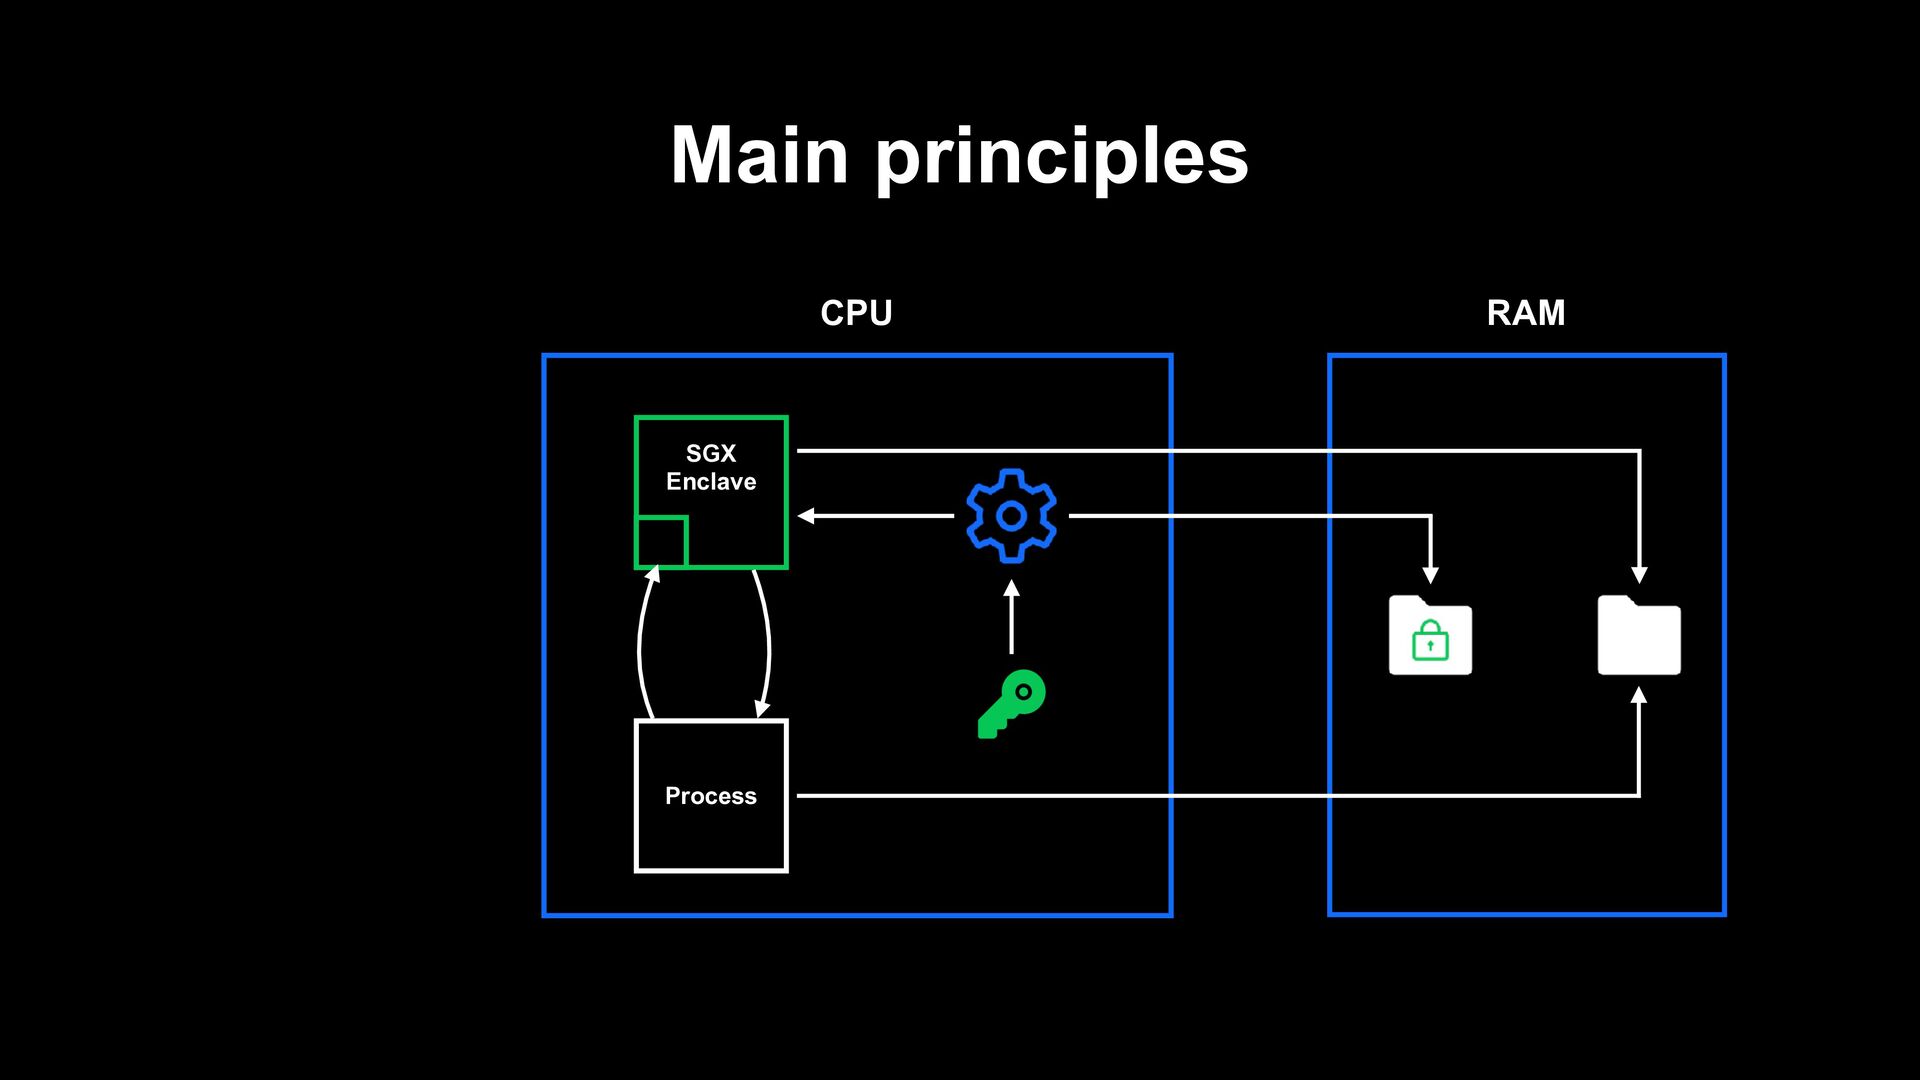
Data Sealing Safe export of secrets from the trusted environment
- SGX only guarantees the authenticity of the code, not its confidentiality - Enclave’s memory encryption is done with a random temporary key Impossible to provision or export secrets with these properties only. -
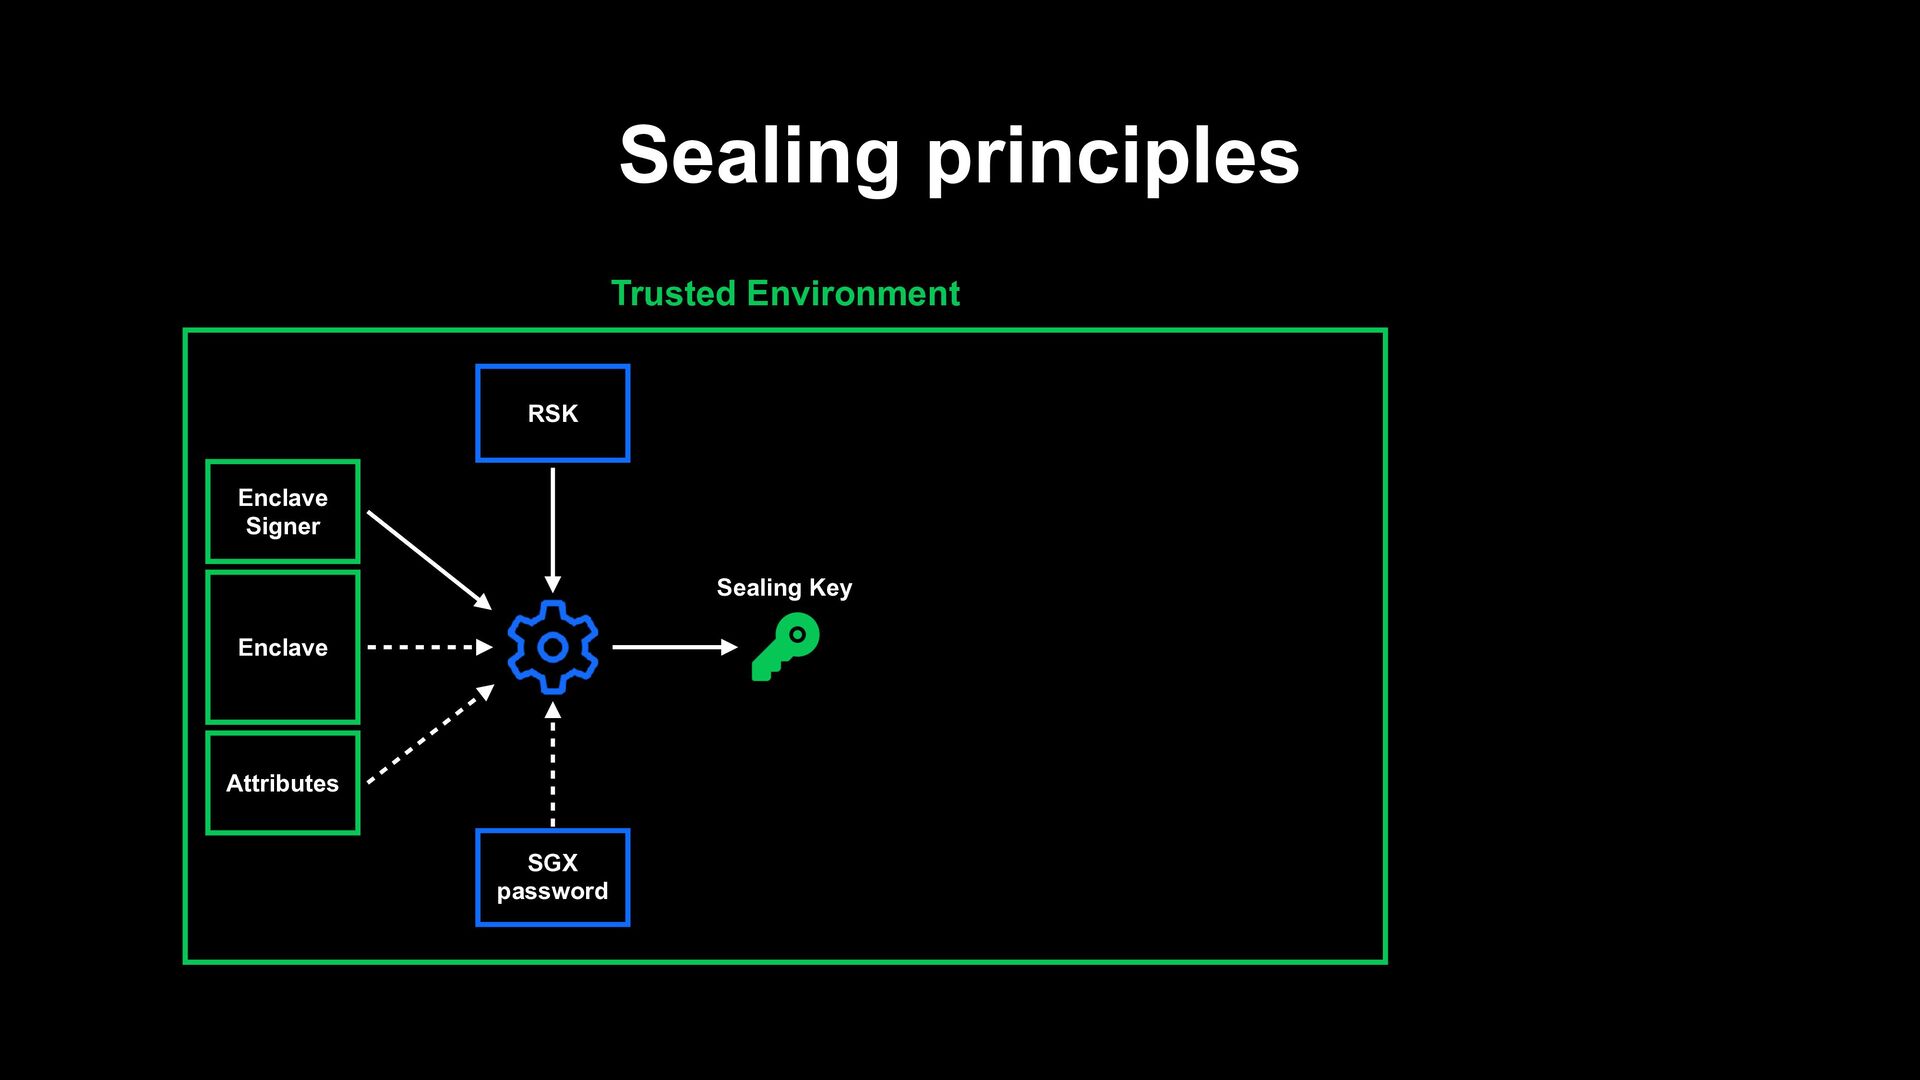
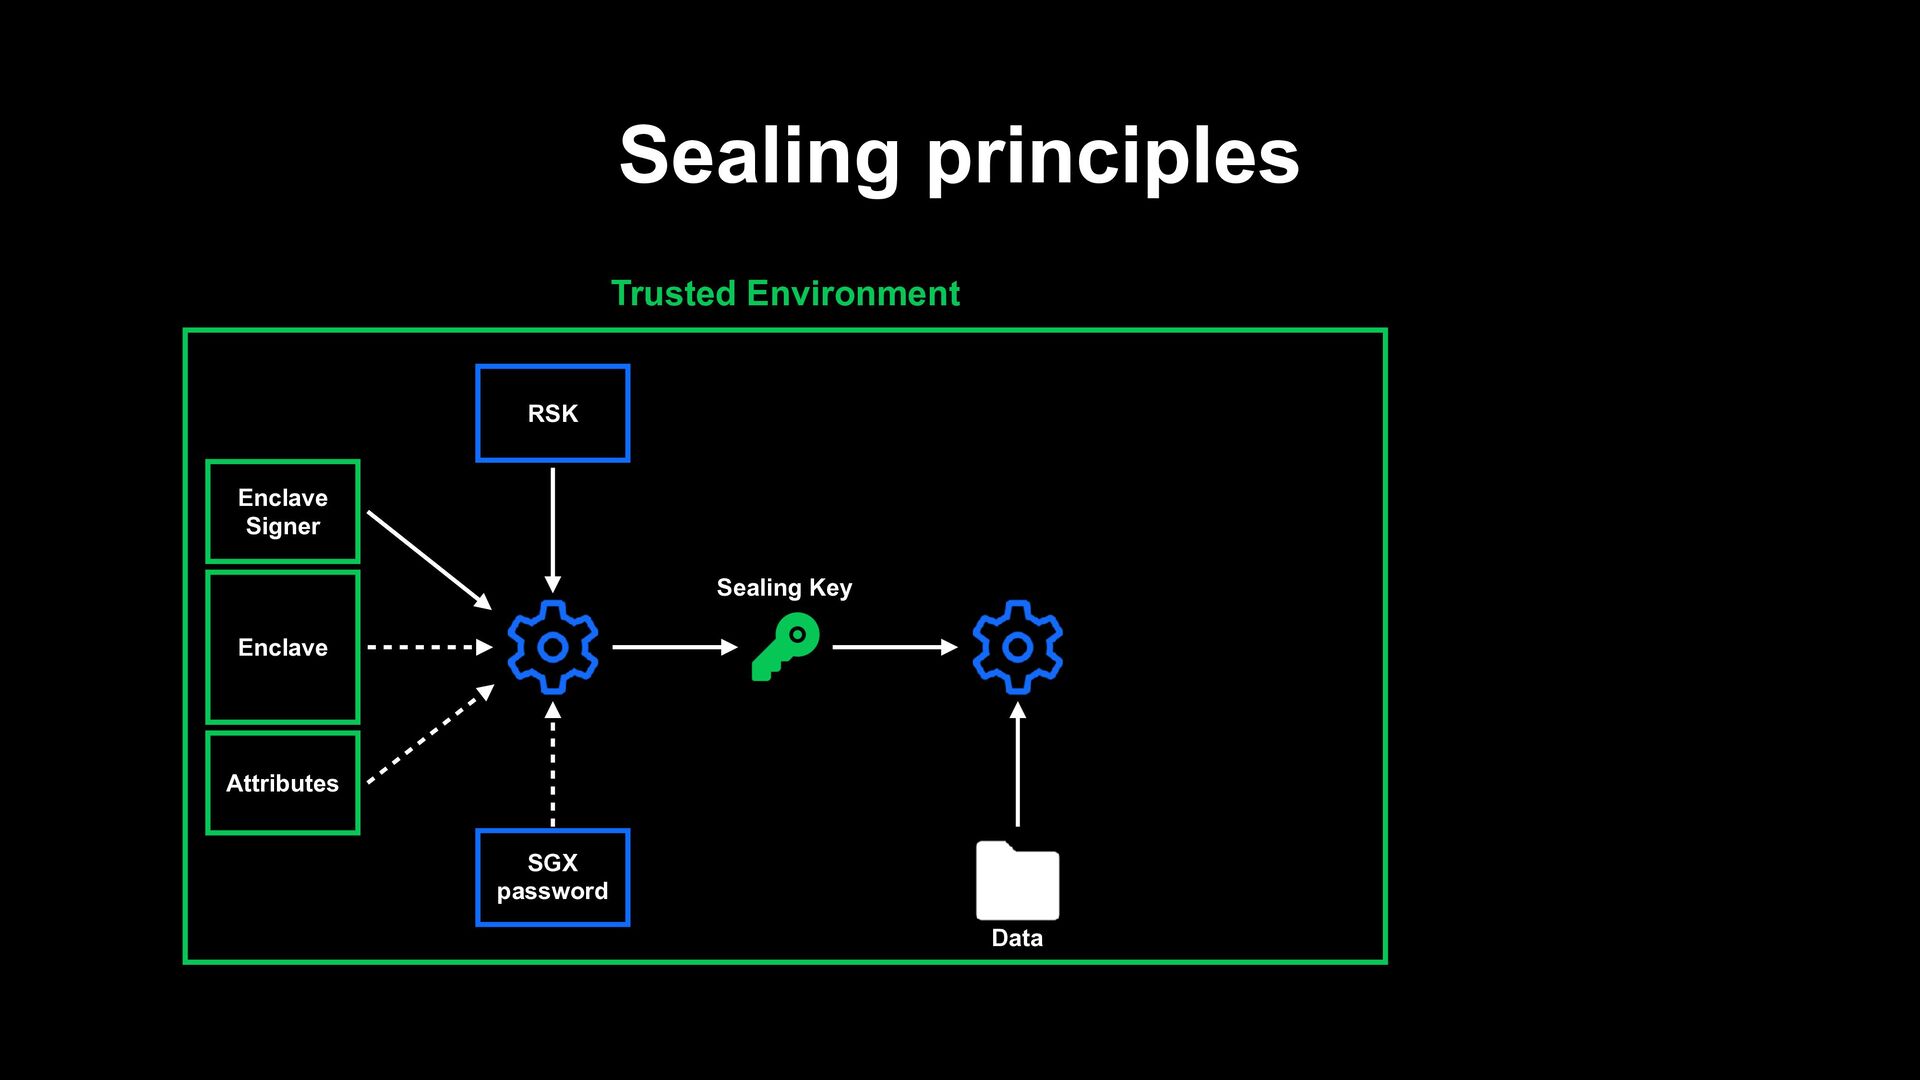
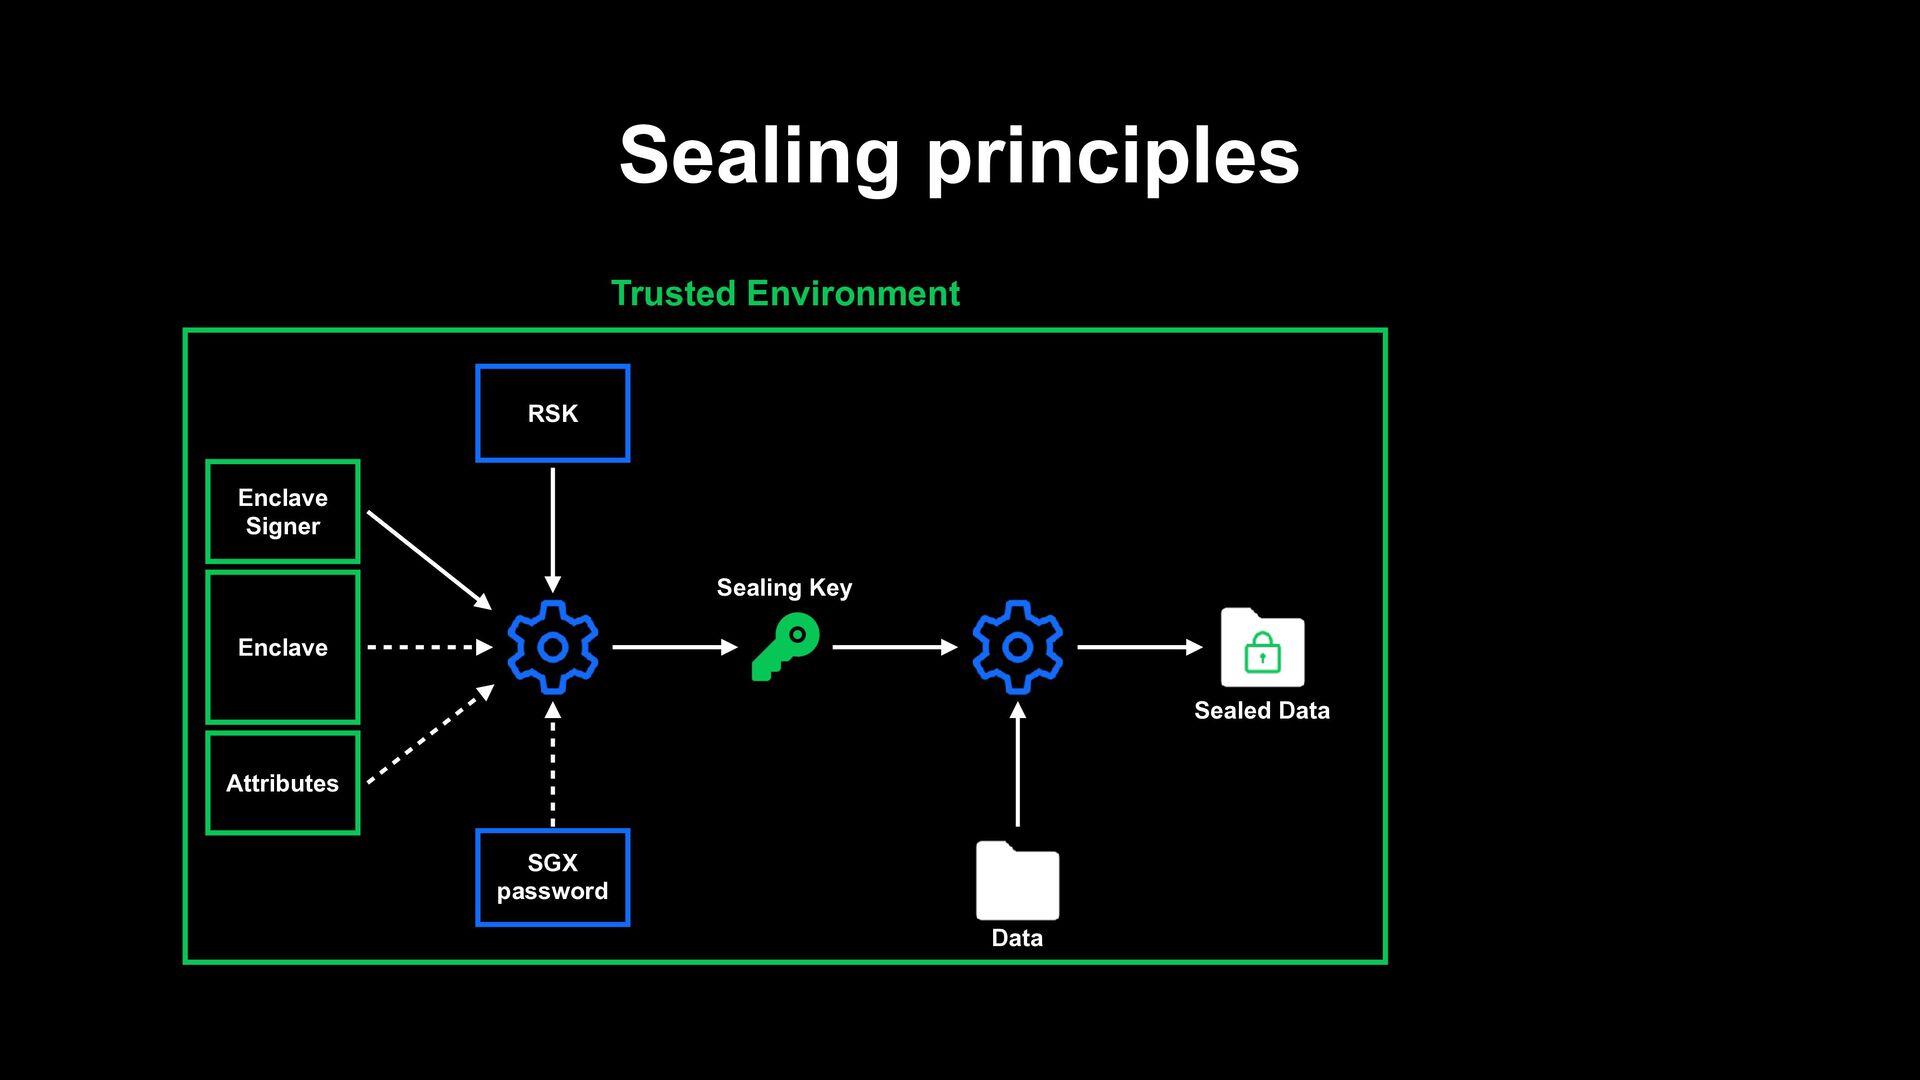
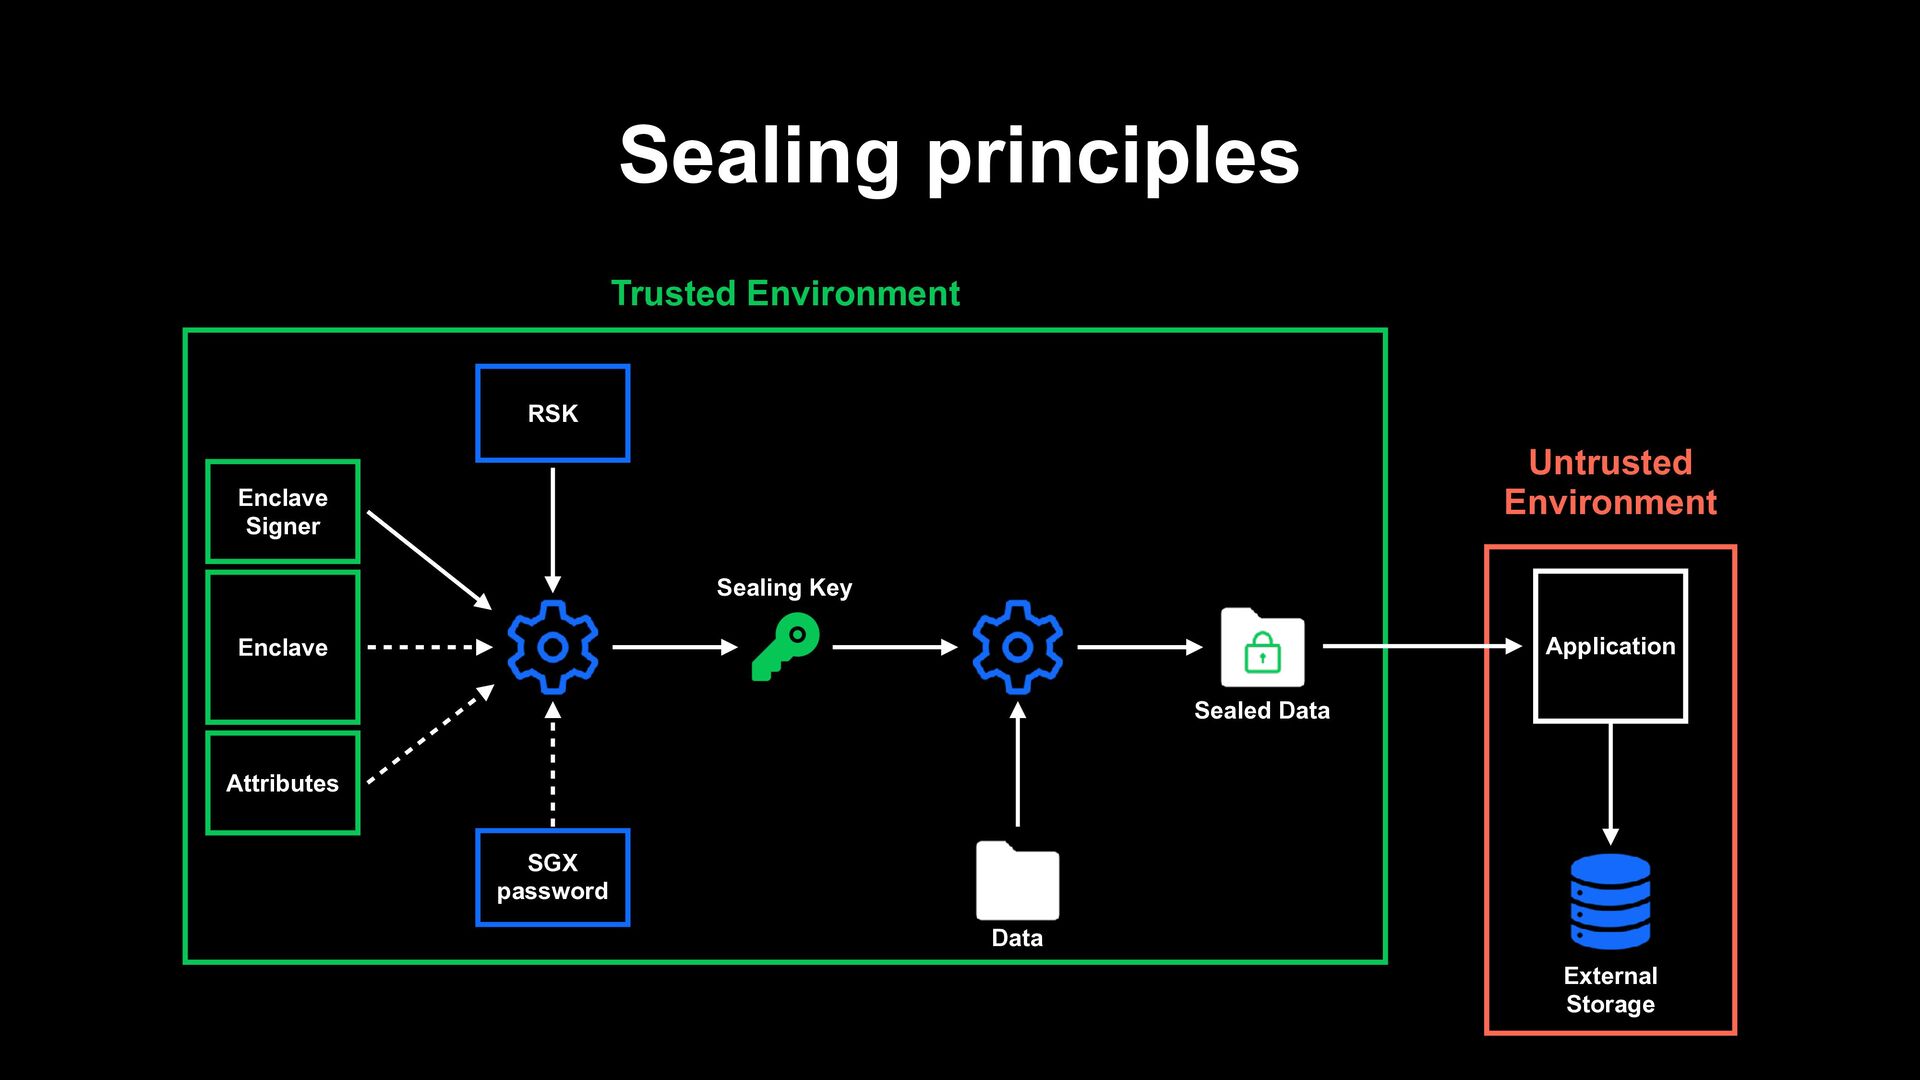
Data Sealing SGX provides a way to safely export data:
- CPUs are provisioned with a Root Sealing Key (RSK), fused in the silicon - The RSK cannot be accessed directly, even by enclaves - Enclaves can request a derivation of the RSK to get their sealing key -
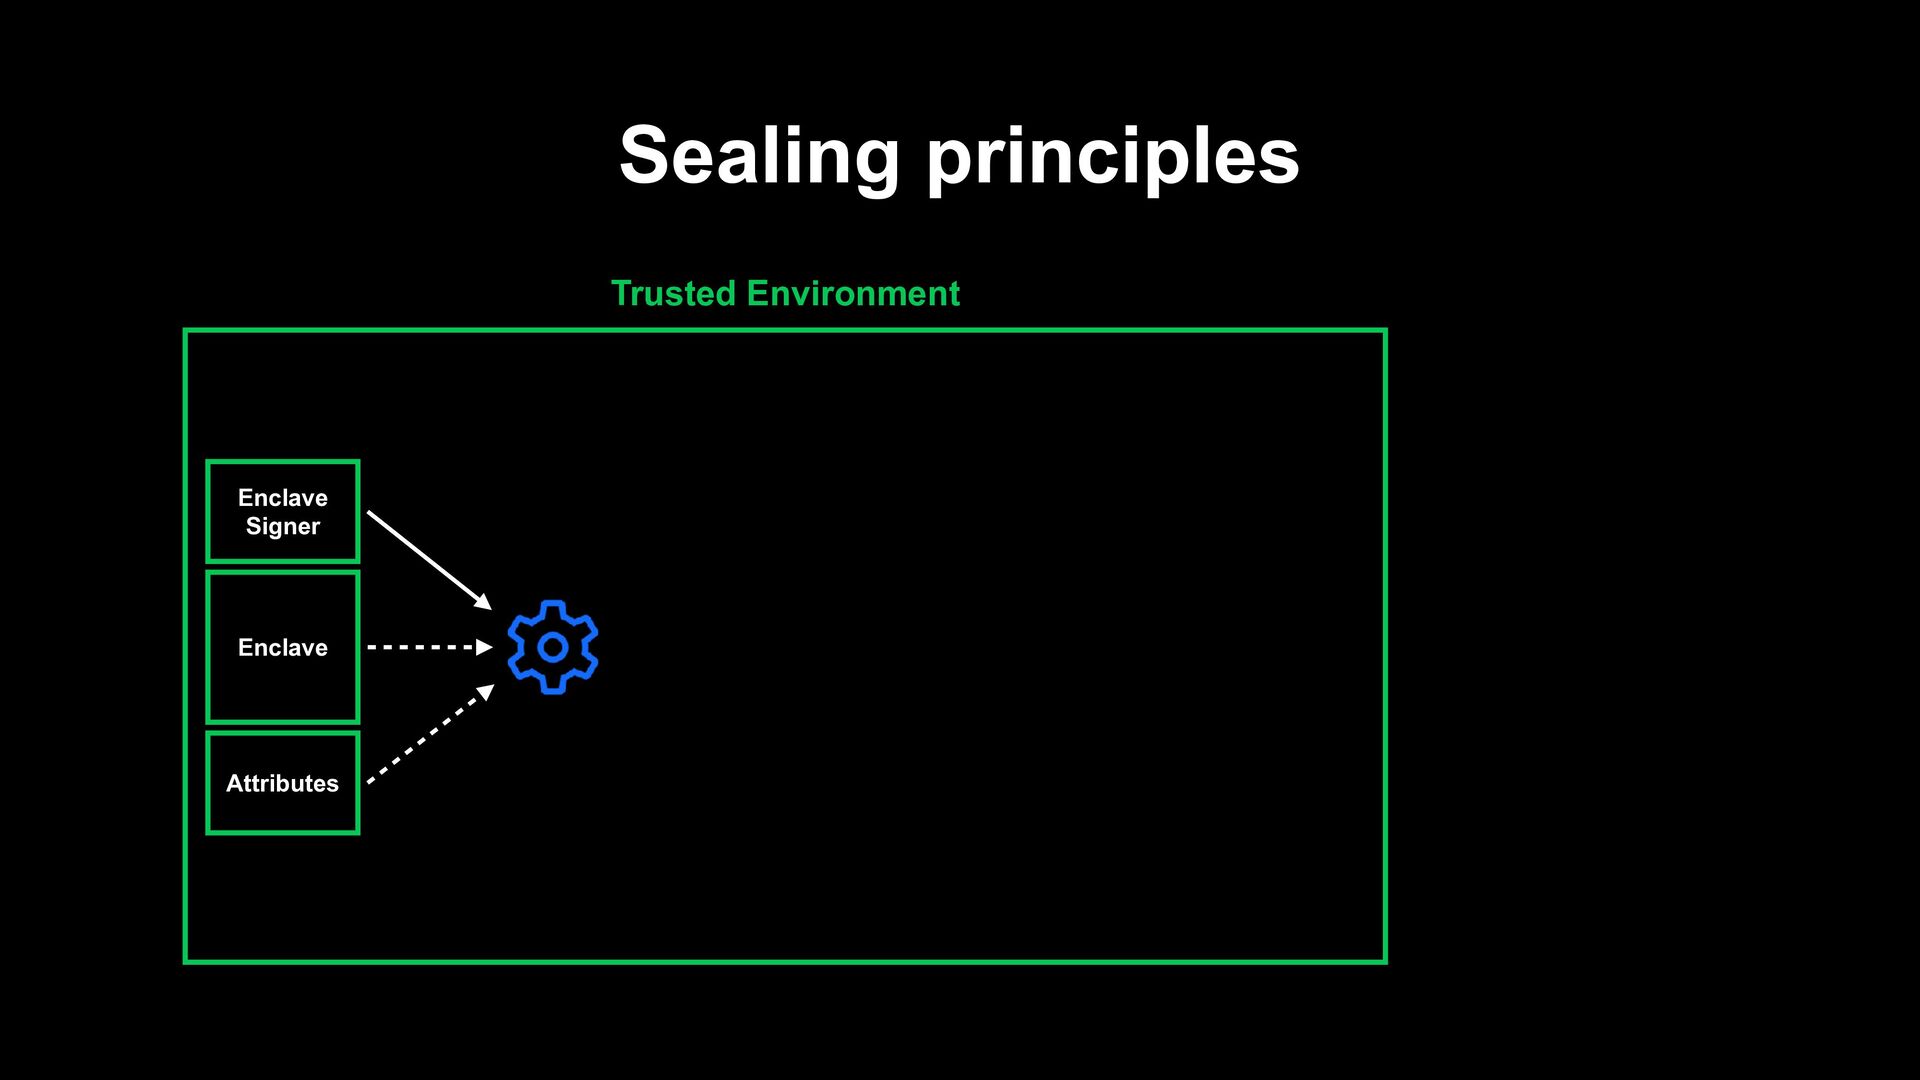
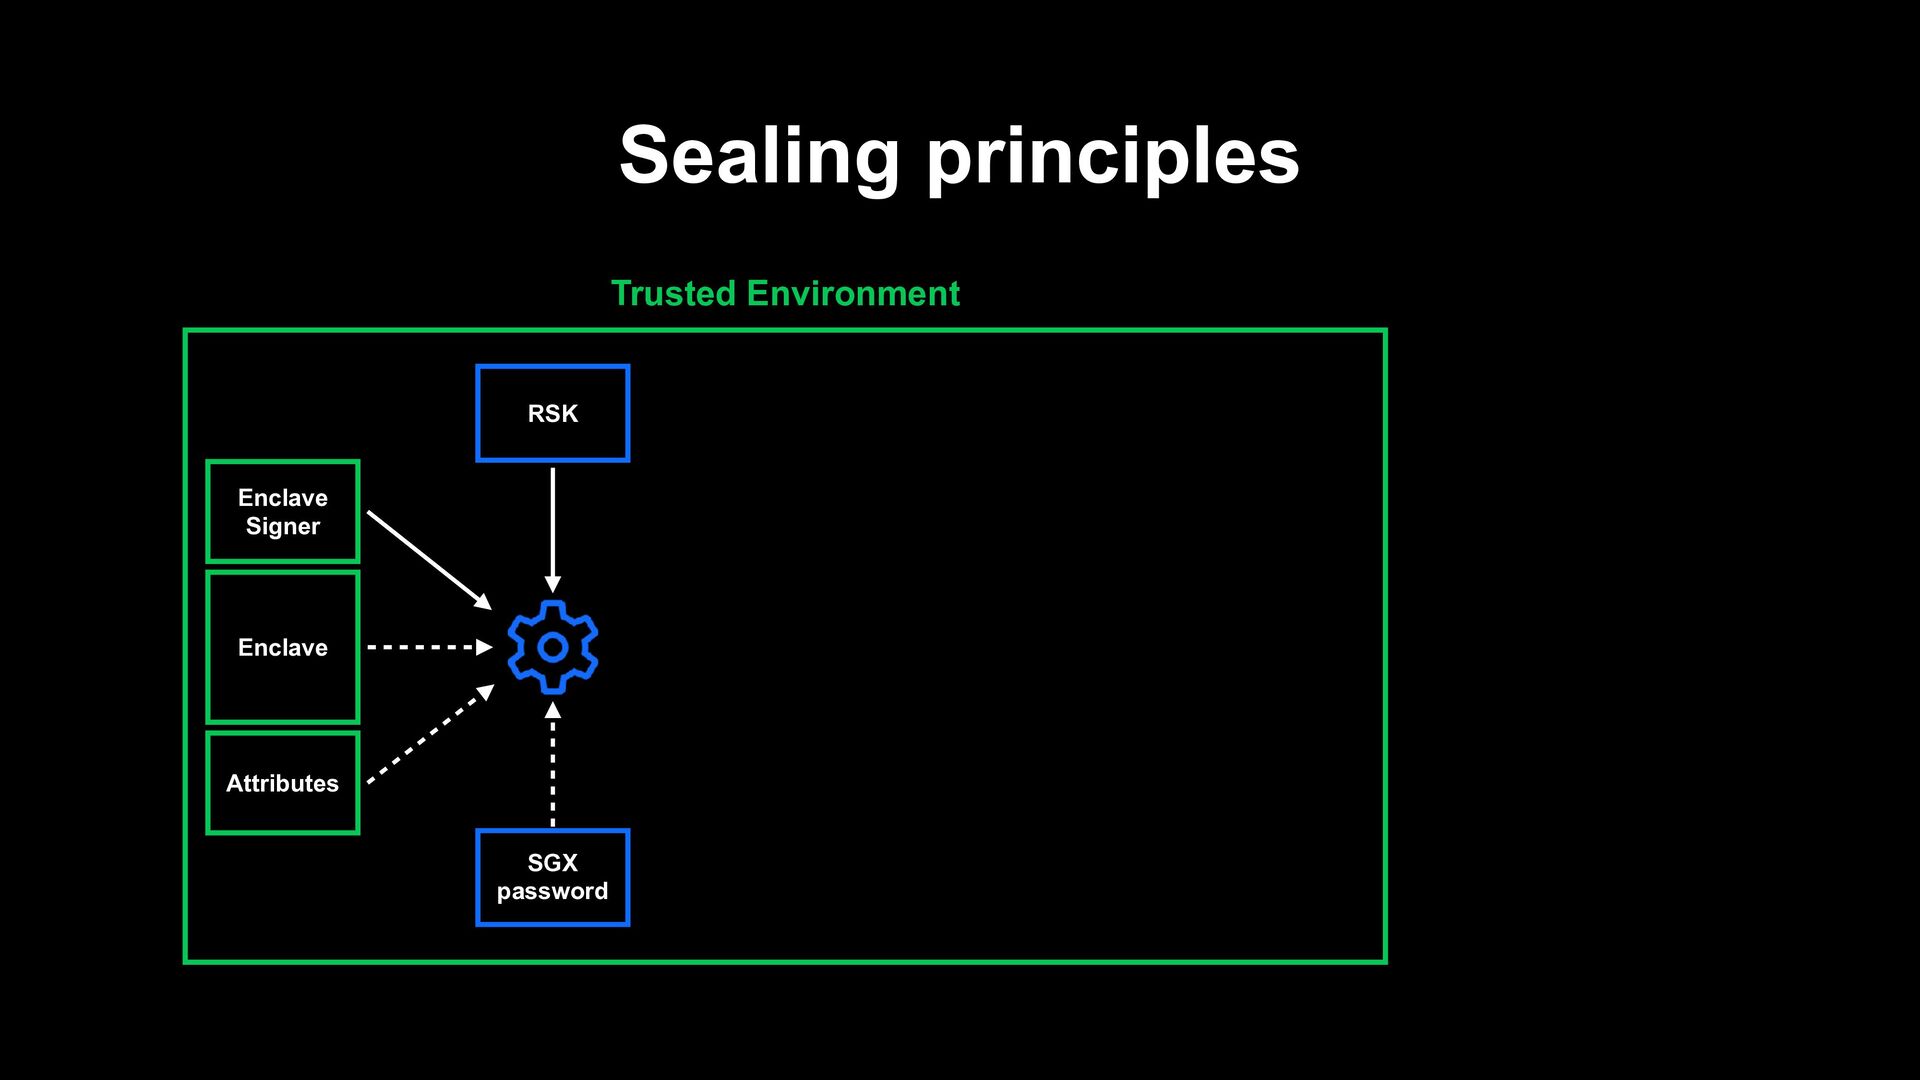
Sealing principles Trusted Environment Enclave Sealing Key SGX password RSK
Enclave Signer Attributes -
Sealing principles Trusted Environment Enclave Sealing Key Data SGX password
RSK Enclave Signer Attributes -
Sealing principles Trusted Environment Enclave Sealing Key Sealed Data Data
SGX password RSK Enclave Signer Attributes -
Sealing principles Trusted Environment Enclave Sealing Key Sealed Data Data
SGX password RSK Untrusted Environment Application External Storage Enclave Signer Attributes -
Code Attestation Provability that the code is running in a
trusted environment - Local attestation: attestation between 2 enclaves on the same machine - Remote attestation: attestation between an enclave and a remote 3rd party -
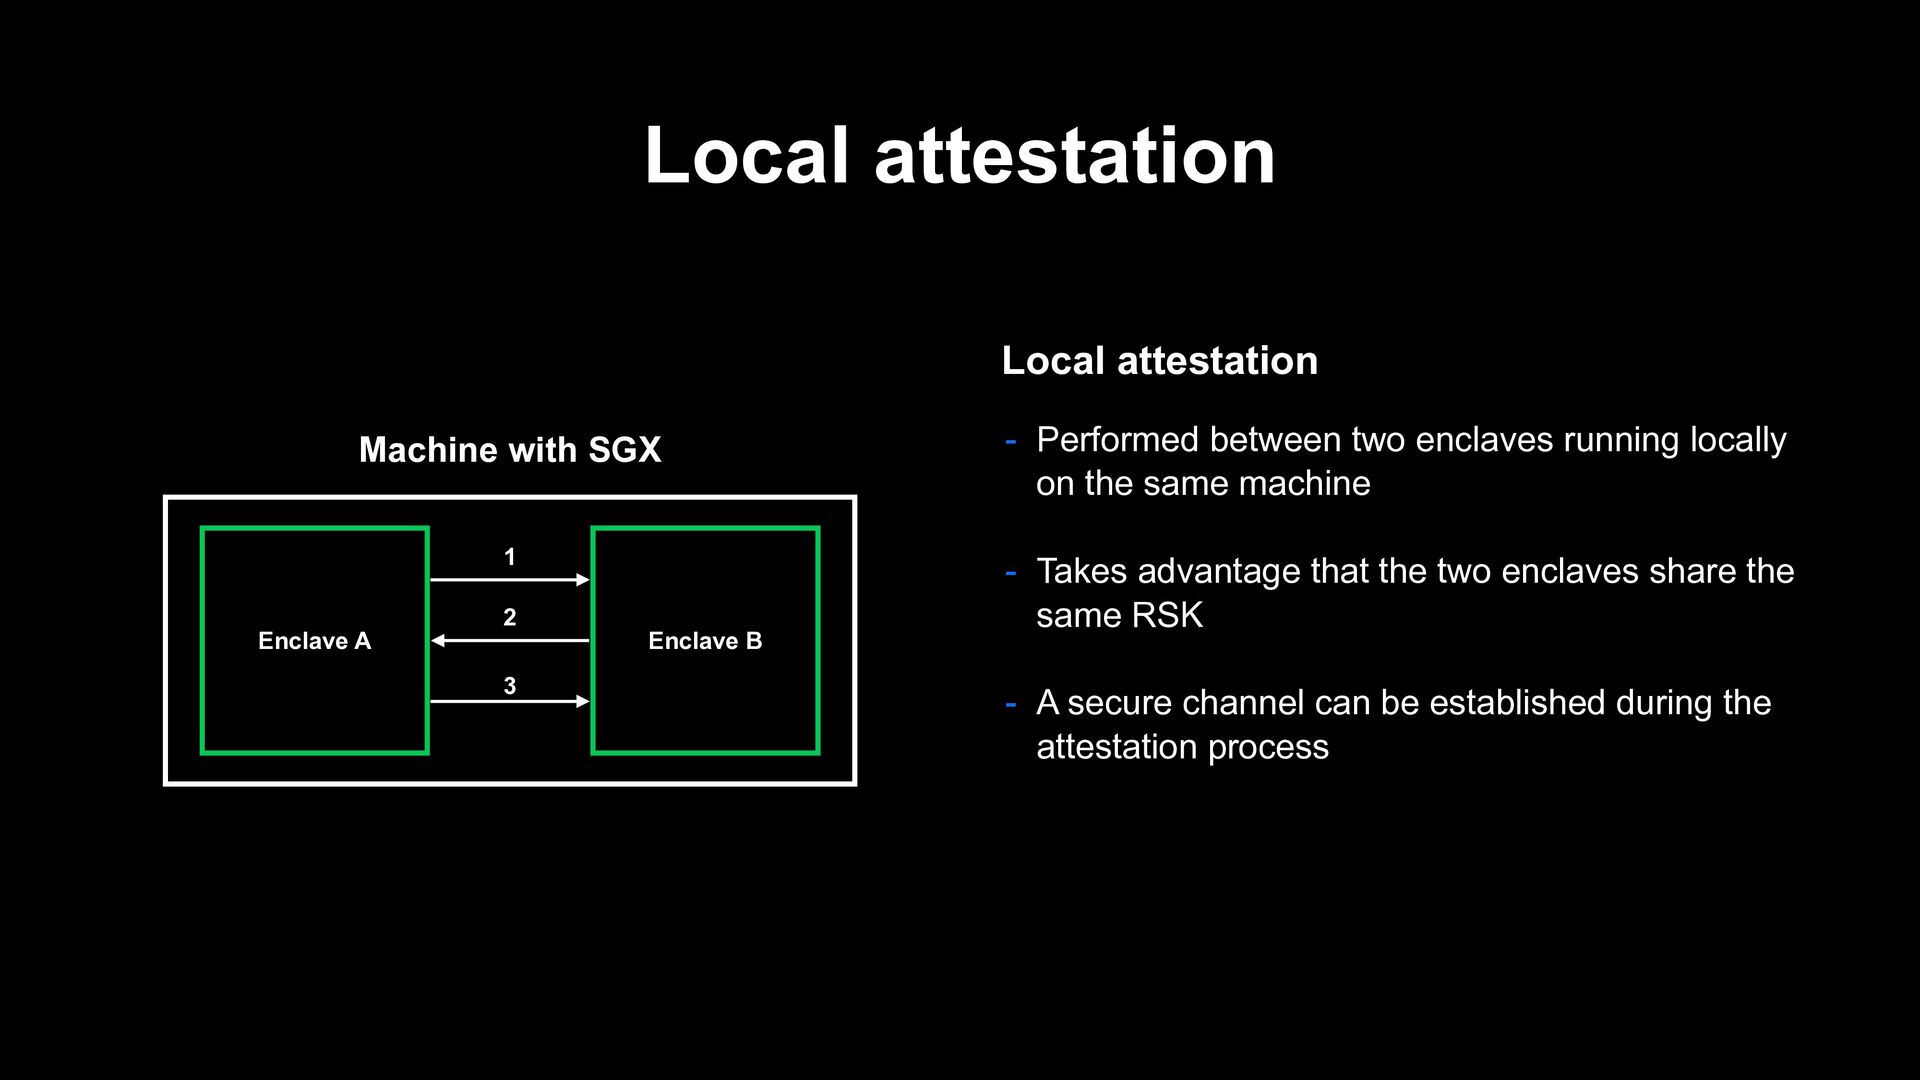
Local attestation Local attestation Enclave A Enclave B 1 2
3 Machine with SGX - Performed between two enclaves running locally on the same machine - Takes advantage that the two enclaves share the same RSK - A secure channel can be established during the attestation process -
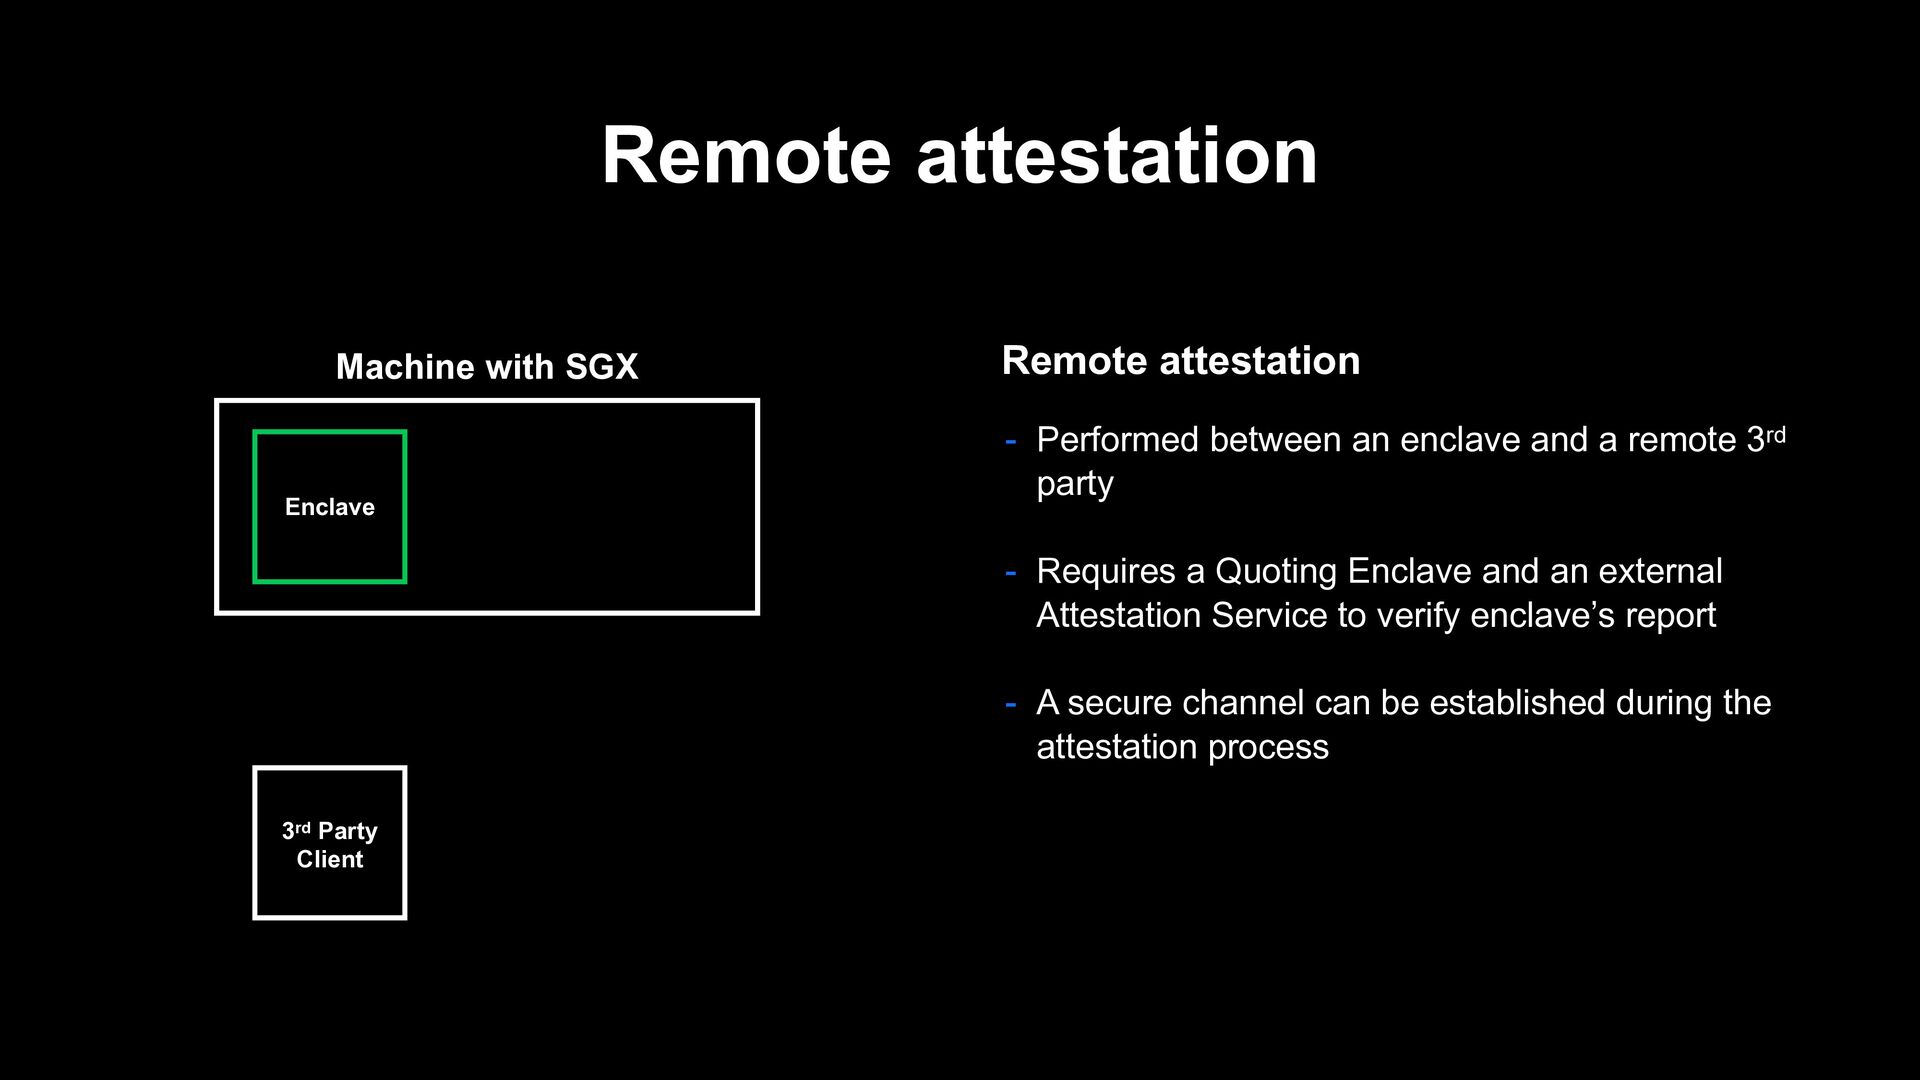
Remote attestation Remote attestation - Performed between an enclave and
a remote 3rd party - Requires a Quoting Enclave and an external Attestation Service to verify enclave’s report - A secure channel can be established during the attestation process Enclave Machine with SGX 3rd Party Client -
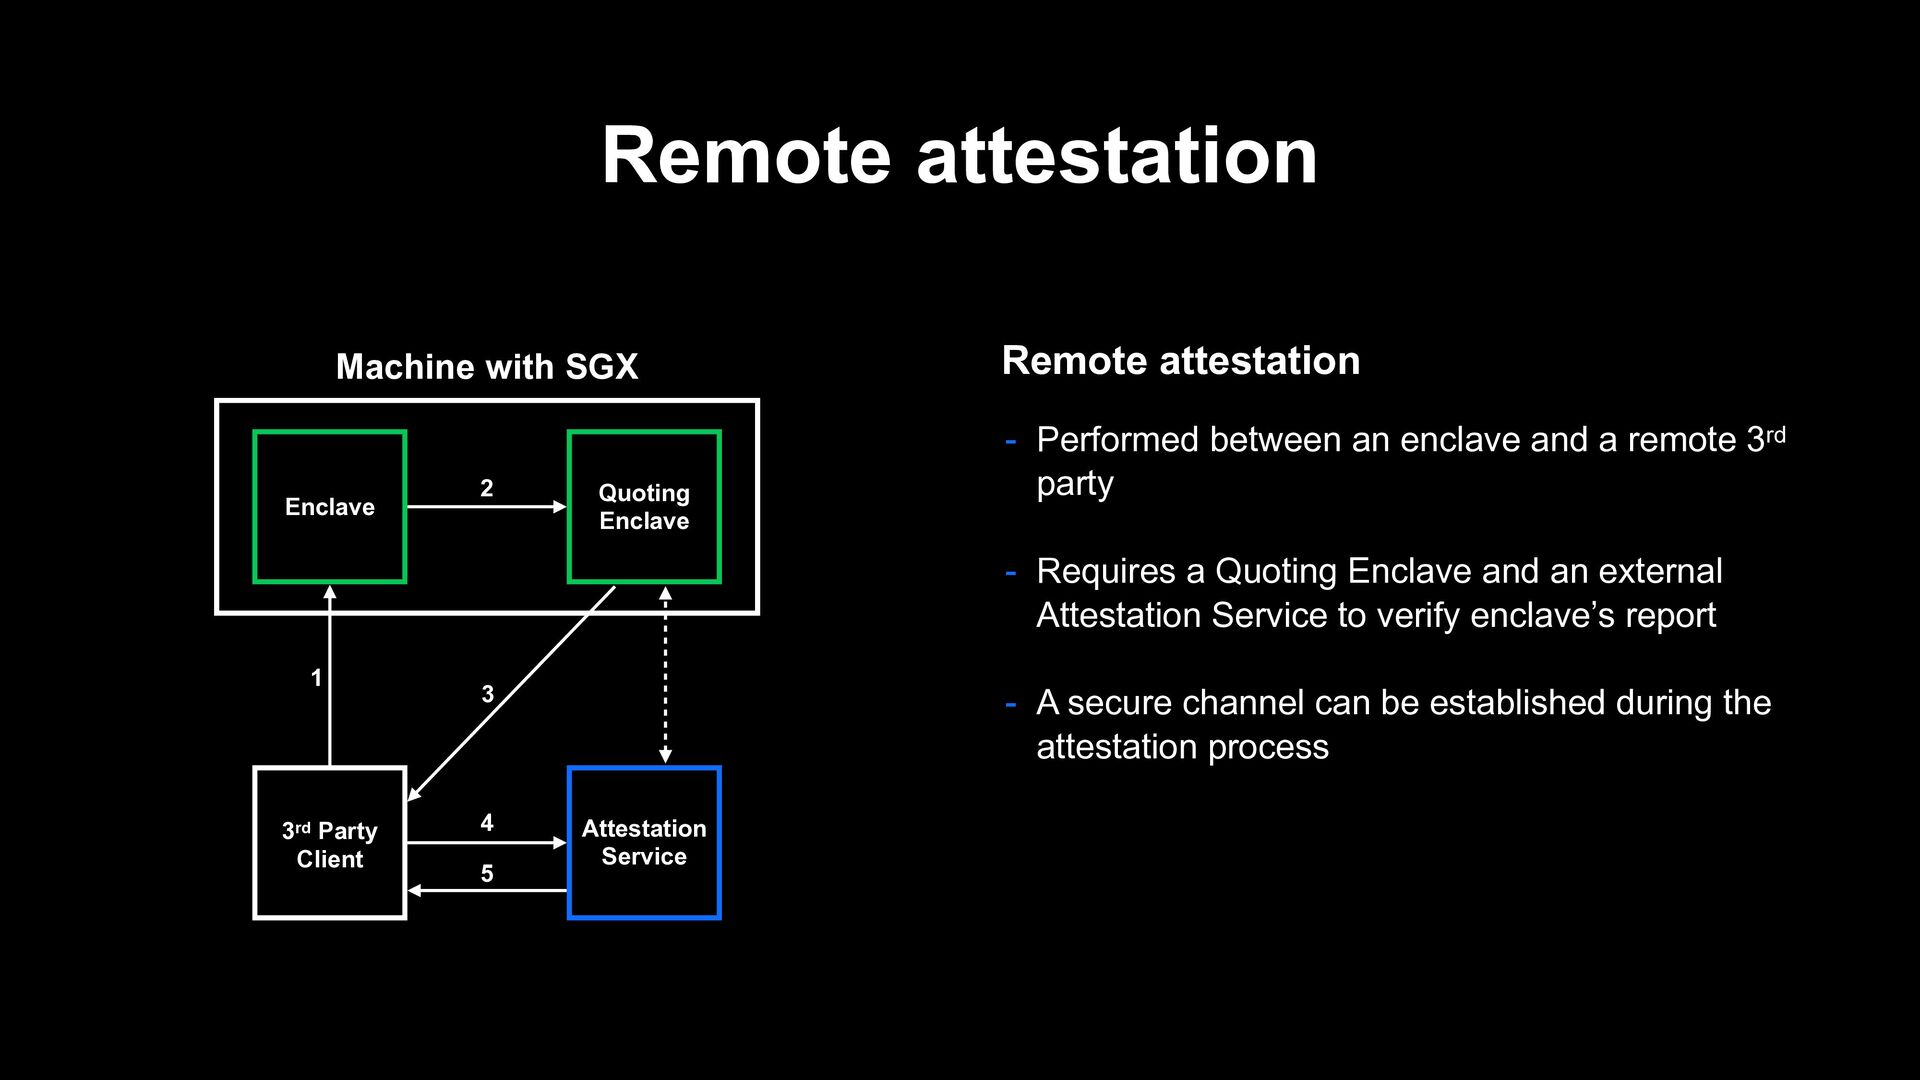
Remote attestation Remote attestation - Performed between an enclave and
a remote 3rd party - Requires a Quoting Enclave and an external Attestation Service to verify enclave’s report - A secure channel can be established during the attestation process Enclave Machine with SGX 3rd Party Client Quoting Enclave 1 2 3 4 5 Attestation Service -
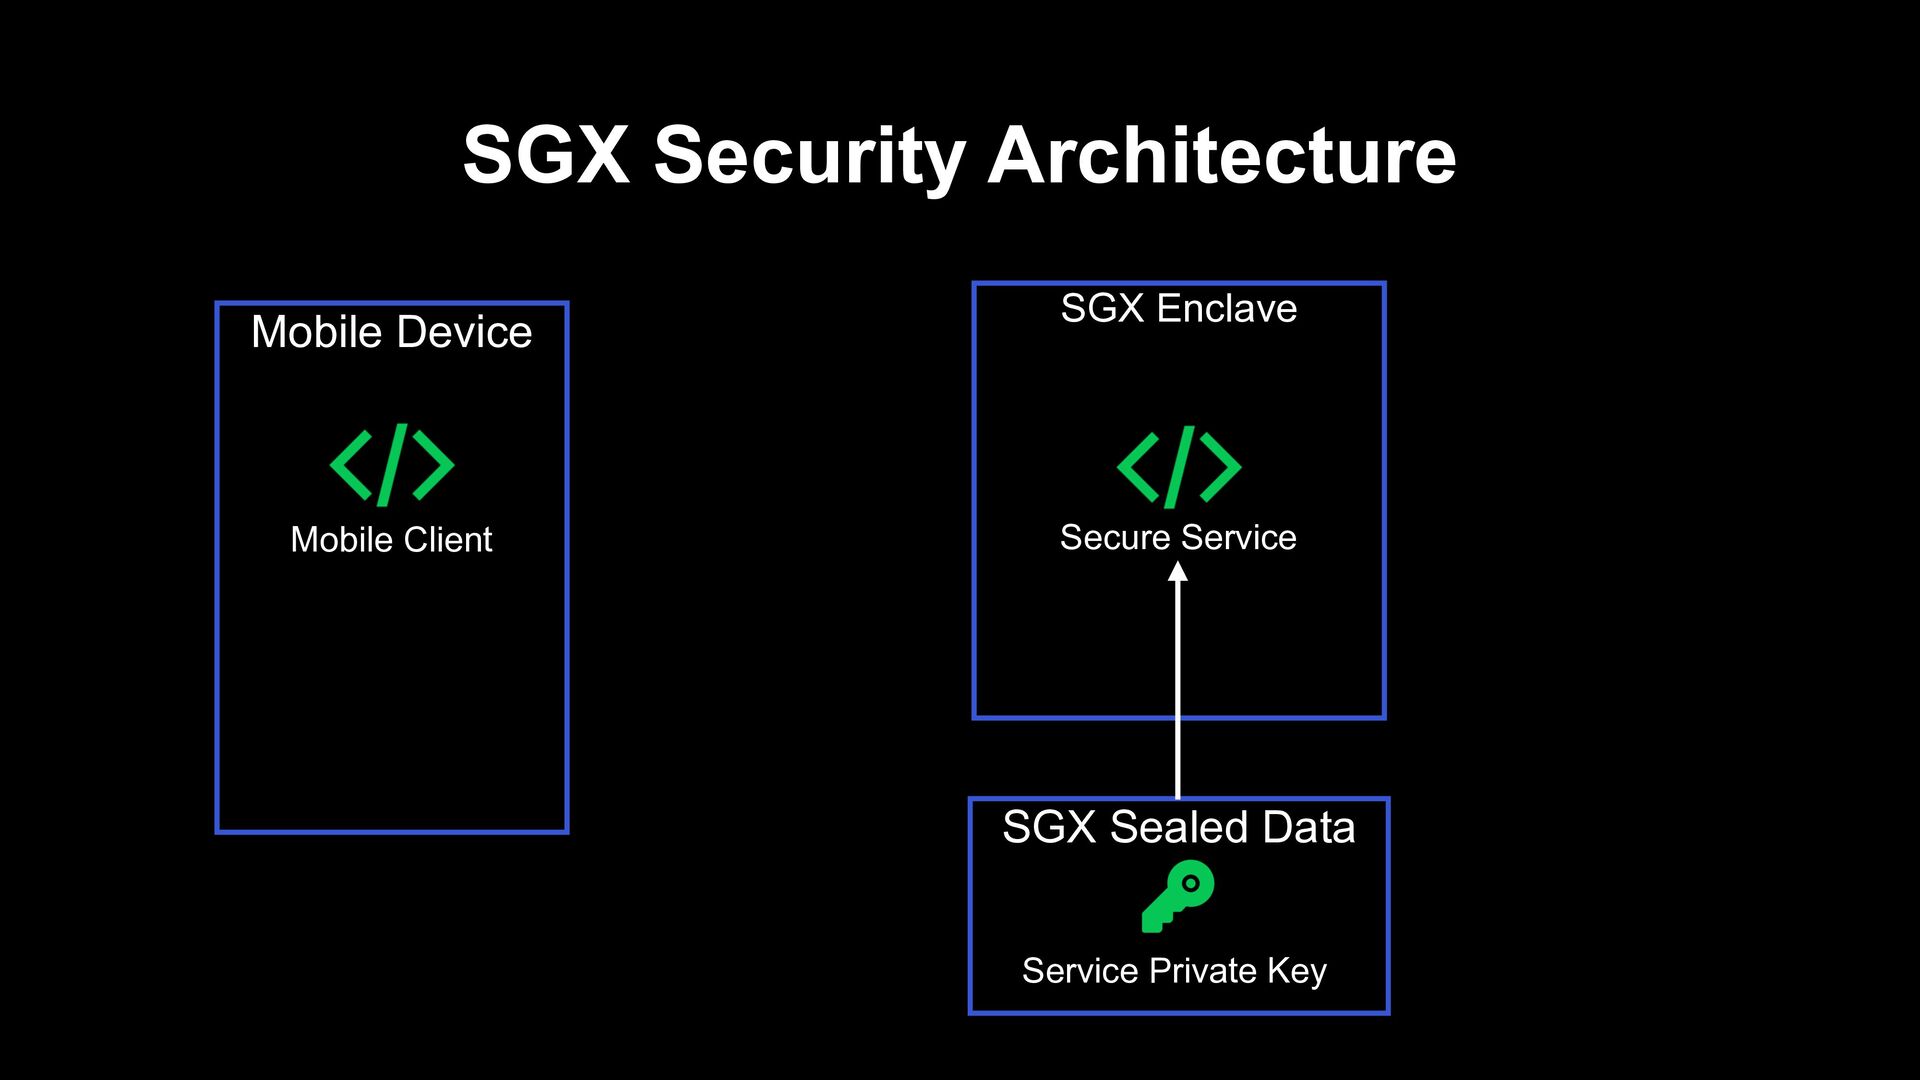
SGX Security Architecture Mobile Device SGX Enclave Secure Service SGX
Sealed Data Service Private Key Mobile Client -
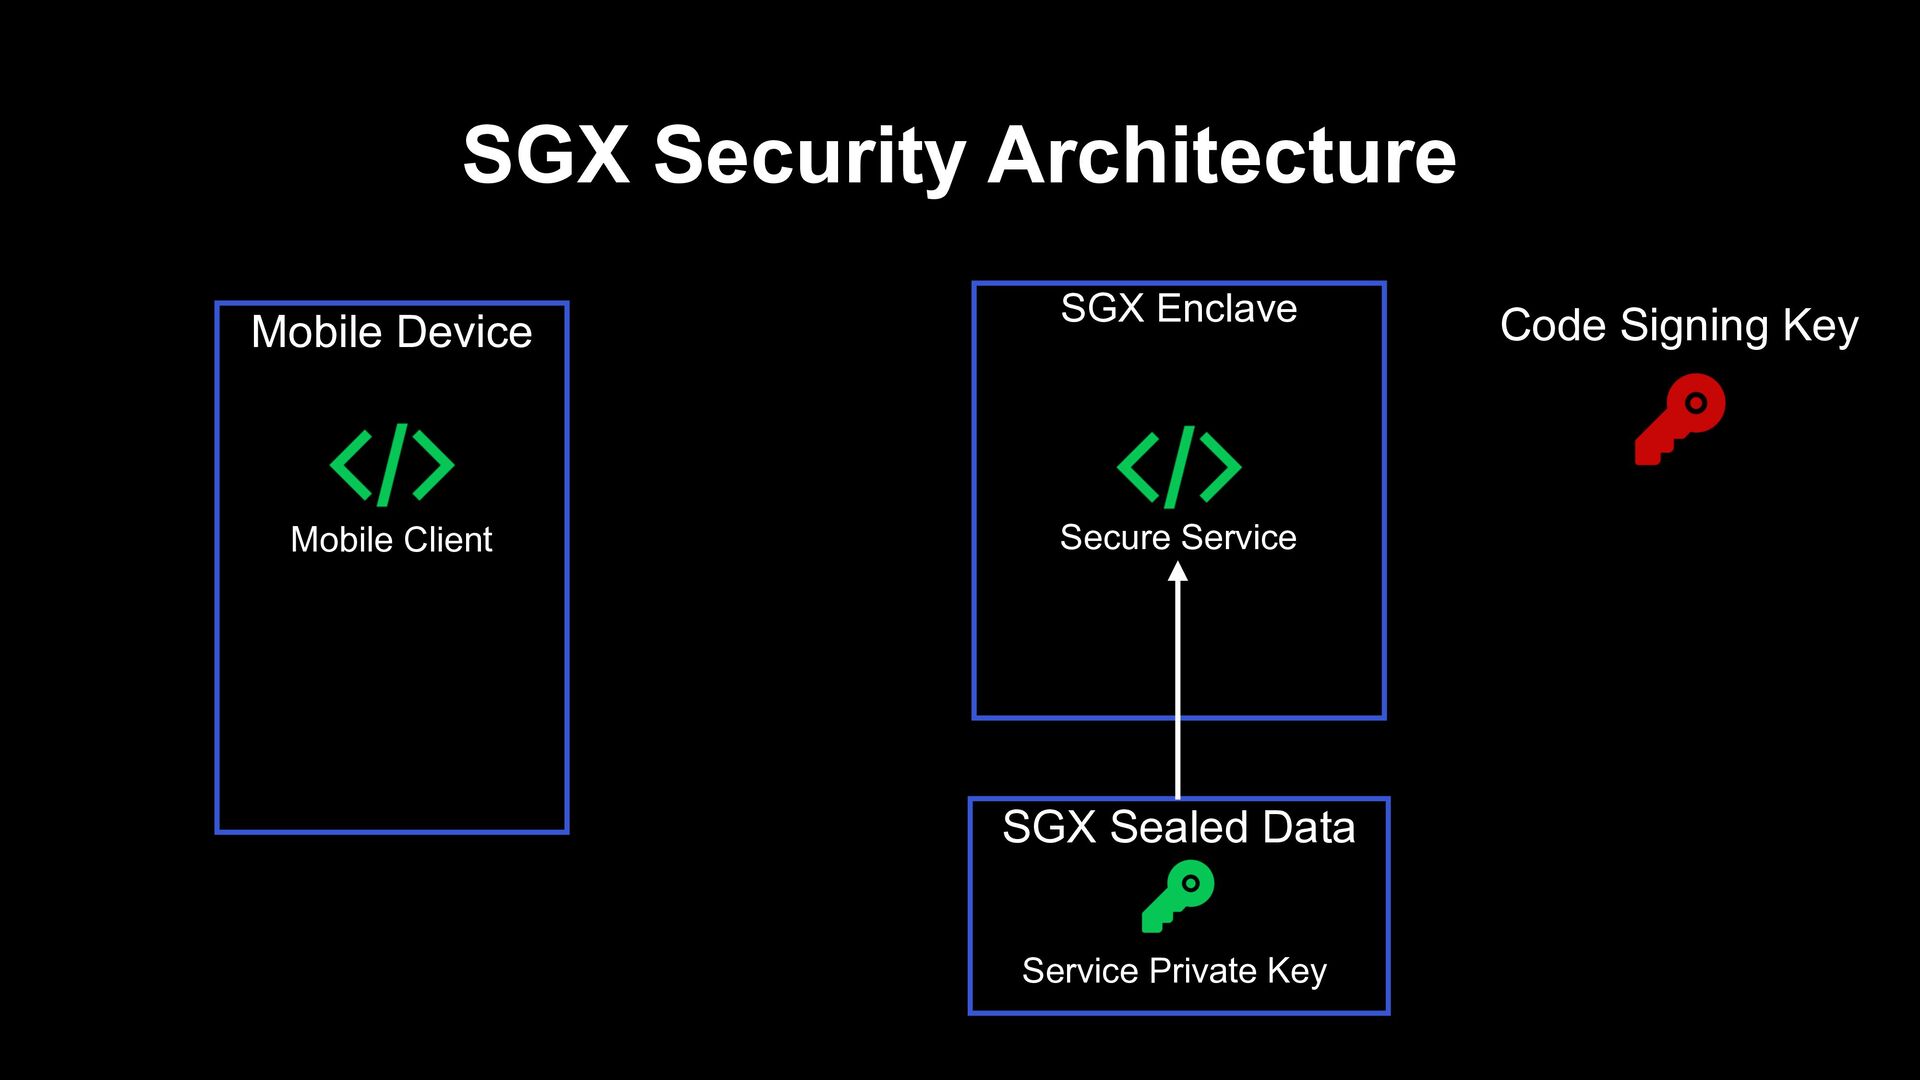
SGX Security Architecture Mobile Device SGX Enclave Secure Service SGX
Sealed Data Service Private Key Code Signing Key Mobile Client -
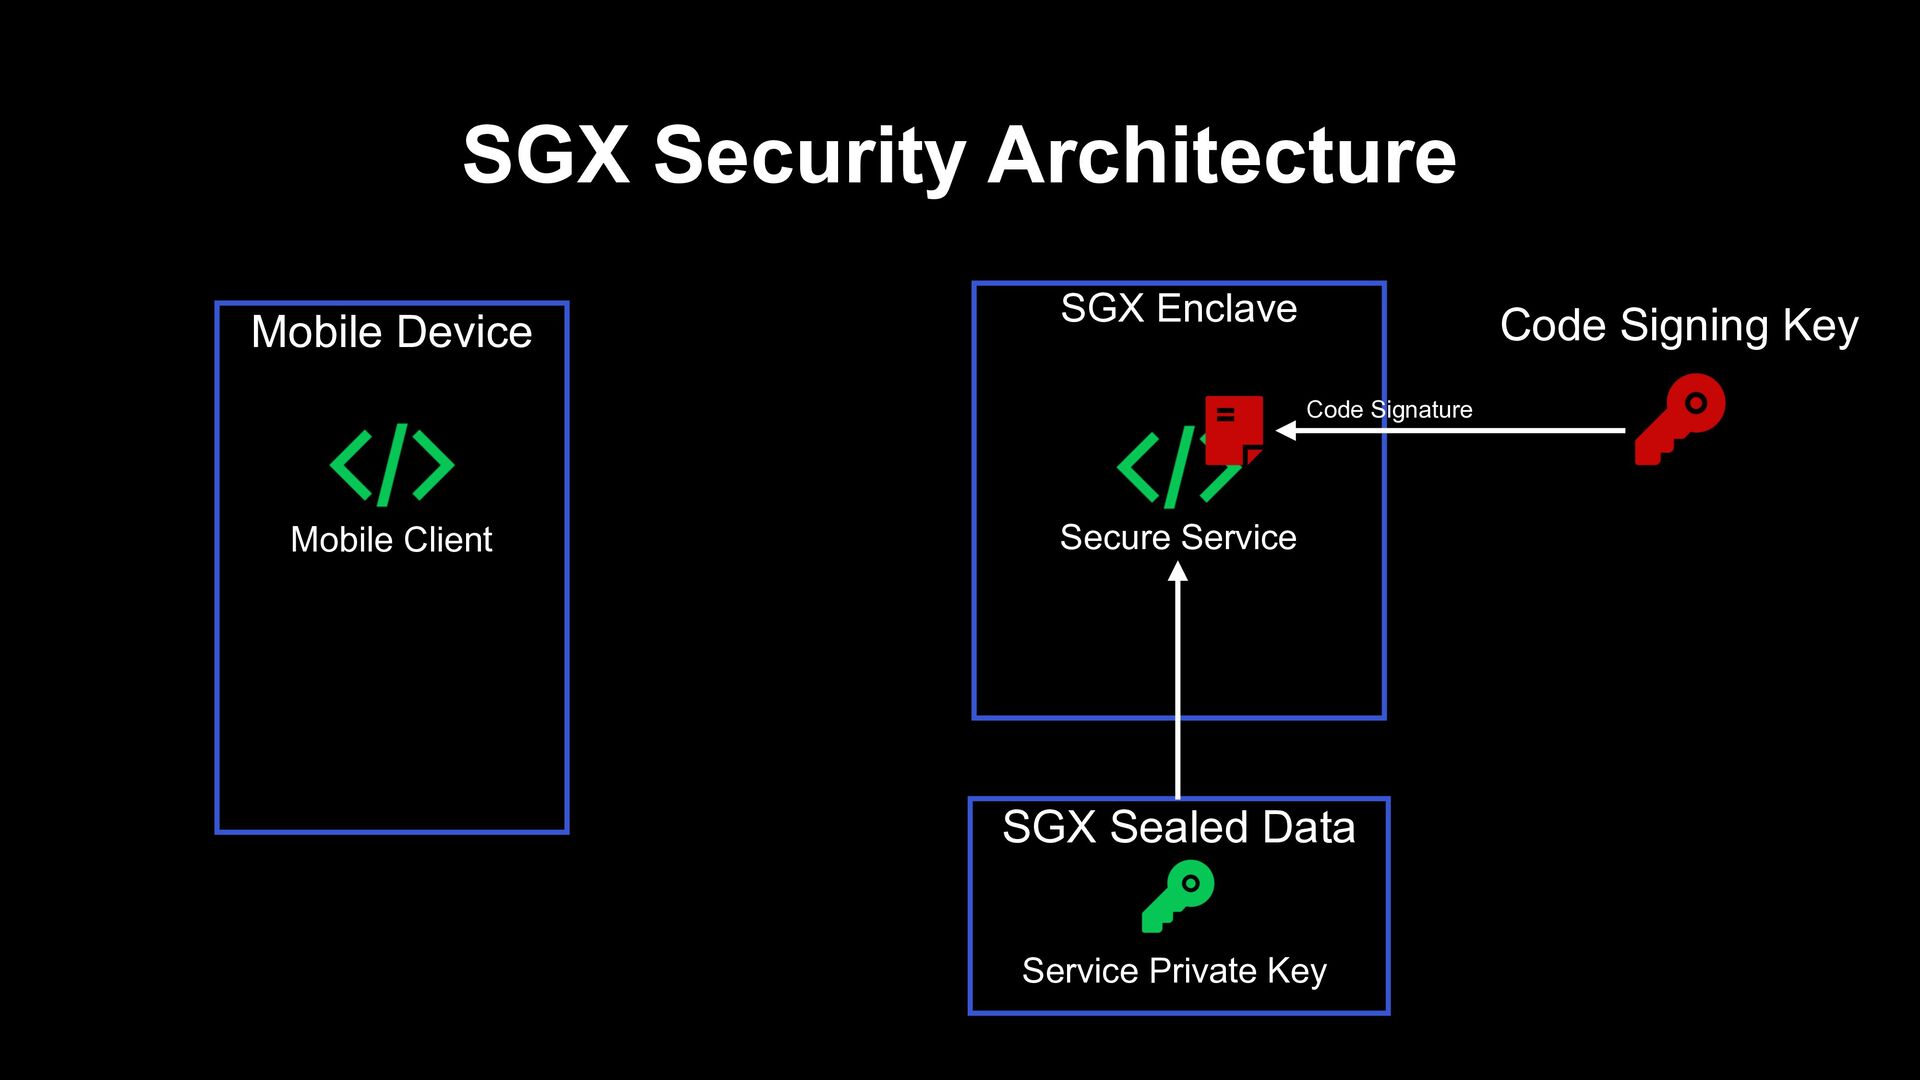
SGX Security Architecture Mobile Device SGX Enclave Secure Service SGX
Sealed Data Service Private Key Code Signing Key Code Signature Mobile Client -
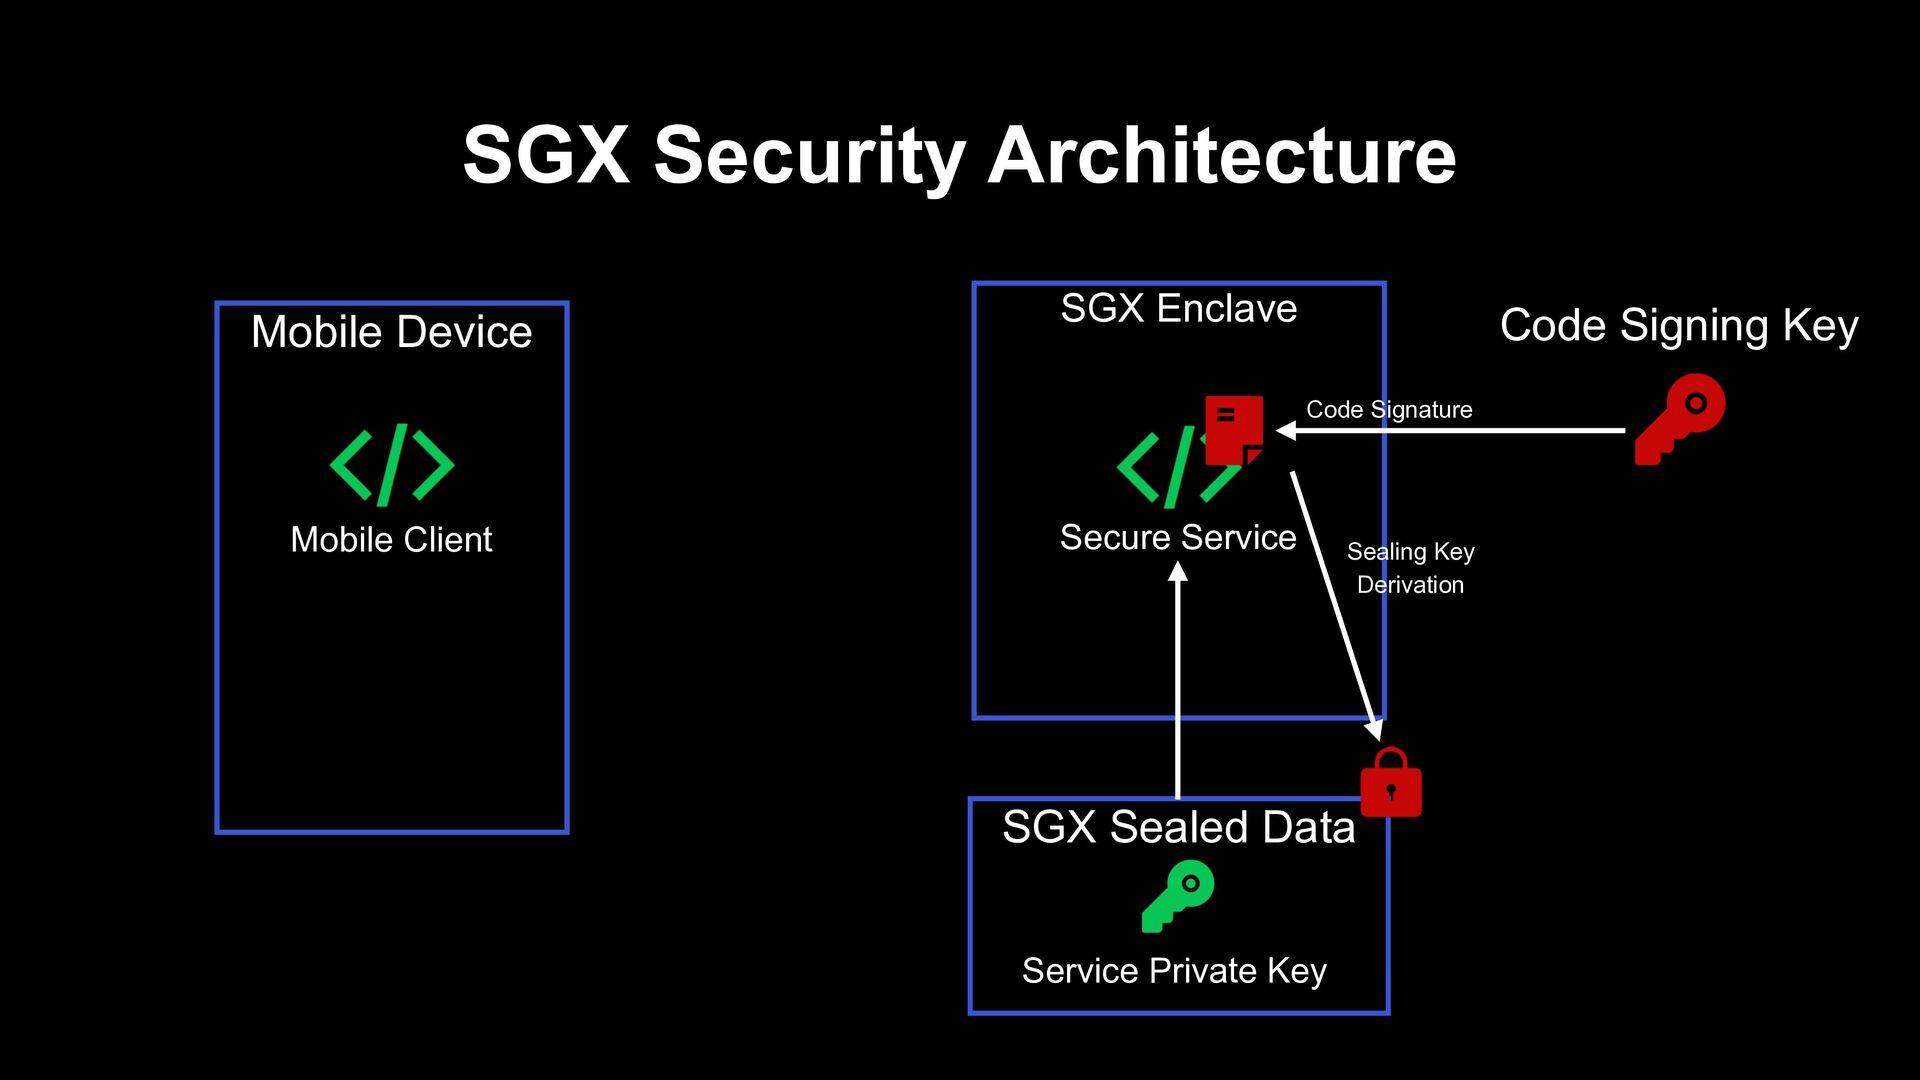
SGX Security Architecture Mobile Device SGX Enclave Secure Service SGX
Sealed Data Service Private Key Code Signing Key Code Signature Sealing Key Derivation Mobile Client -
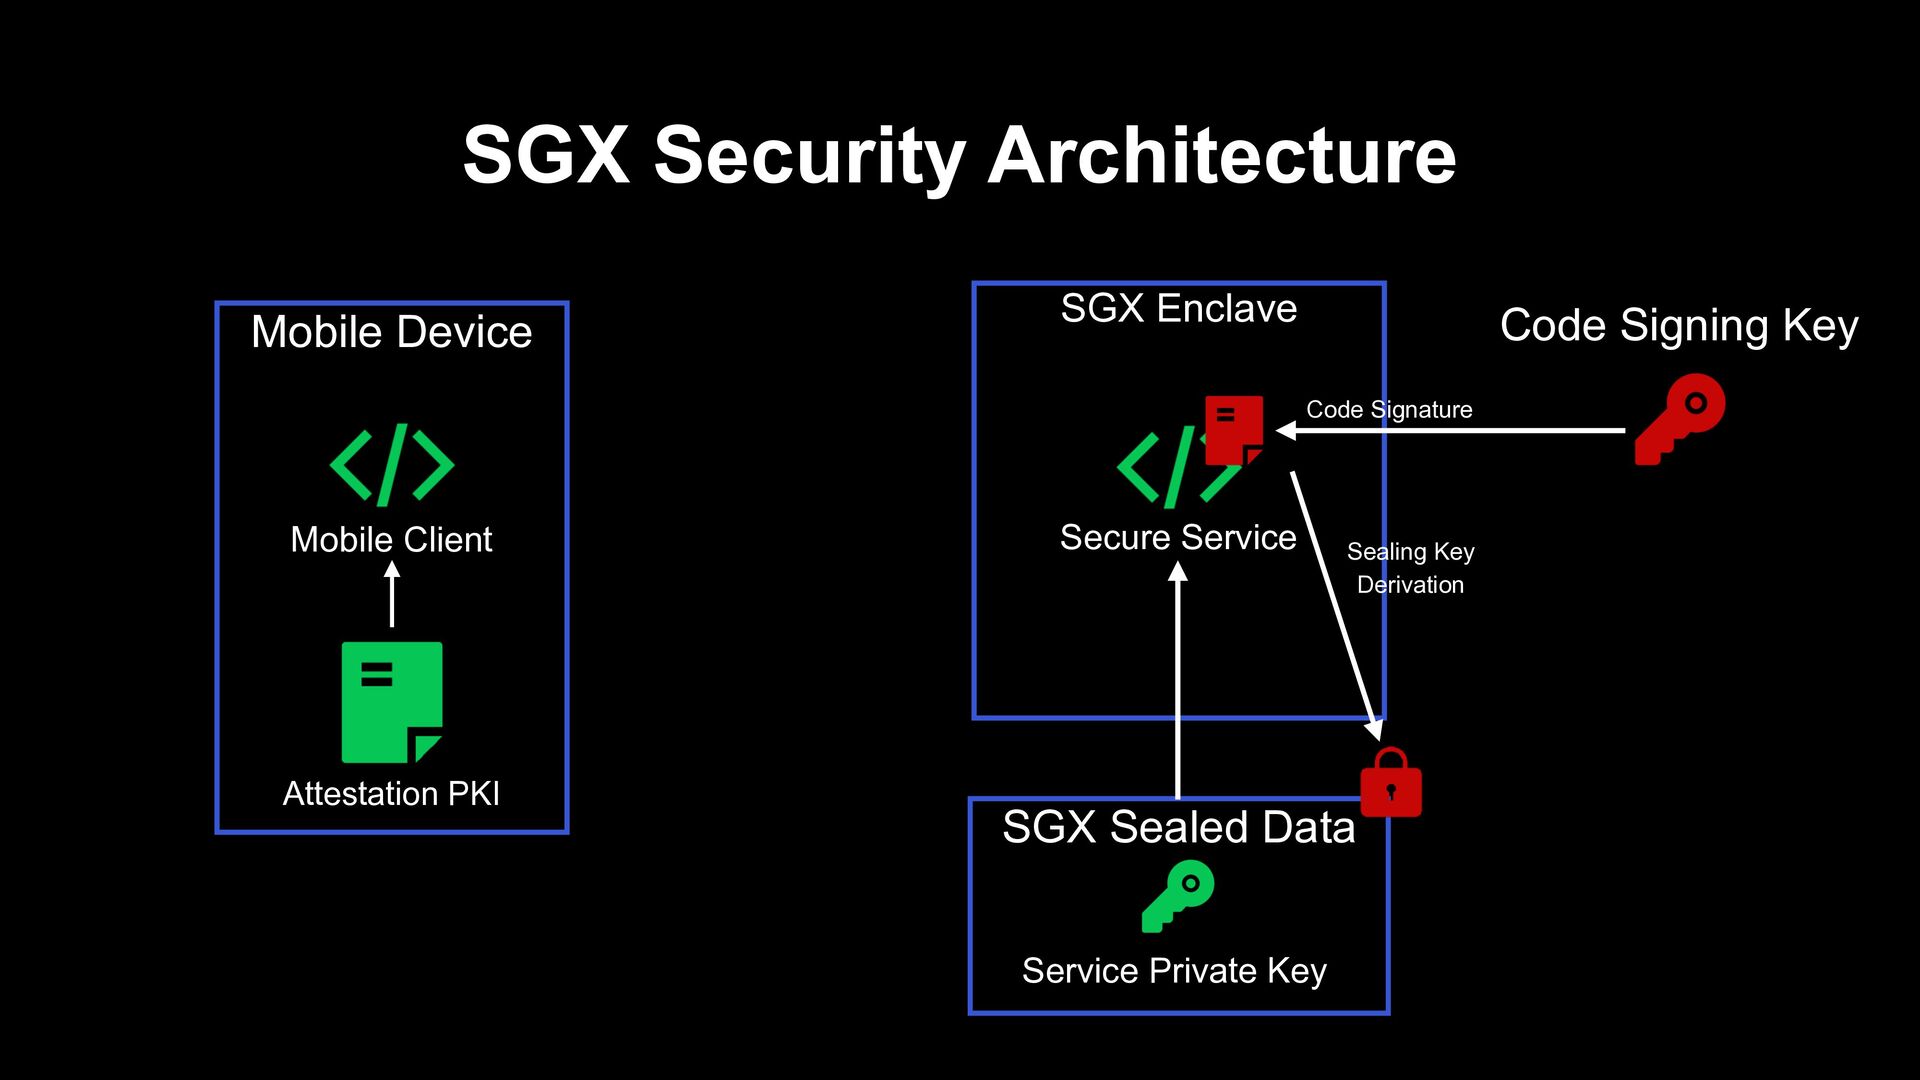
SGX Security Architecture Mobile Device Attestation PKI SGX Enclave Secure
Service SGX Sealed Data Service Private Key Code Signing Key Code Signature Sealing Key Derivation Mobile Client -
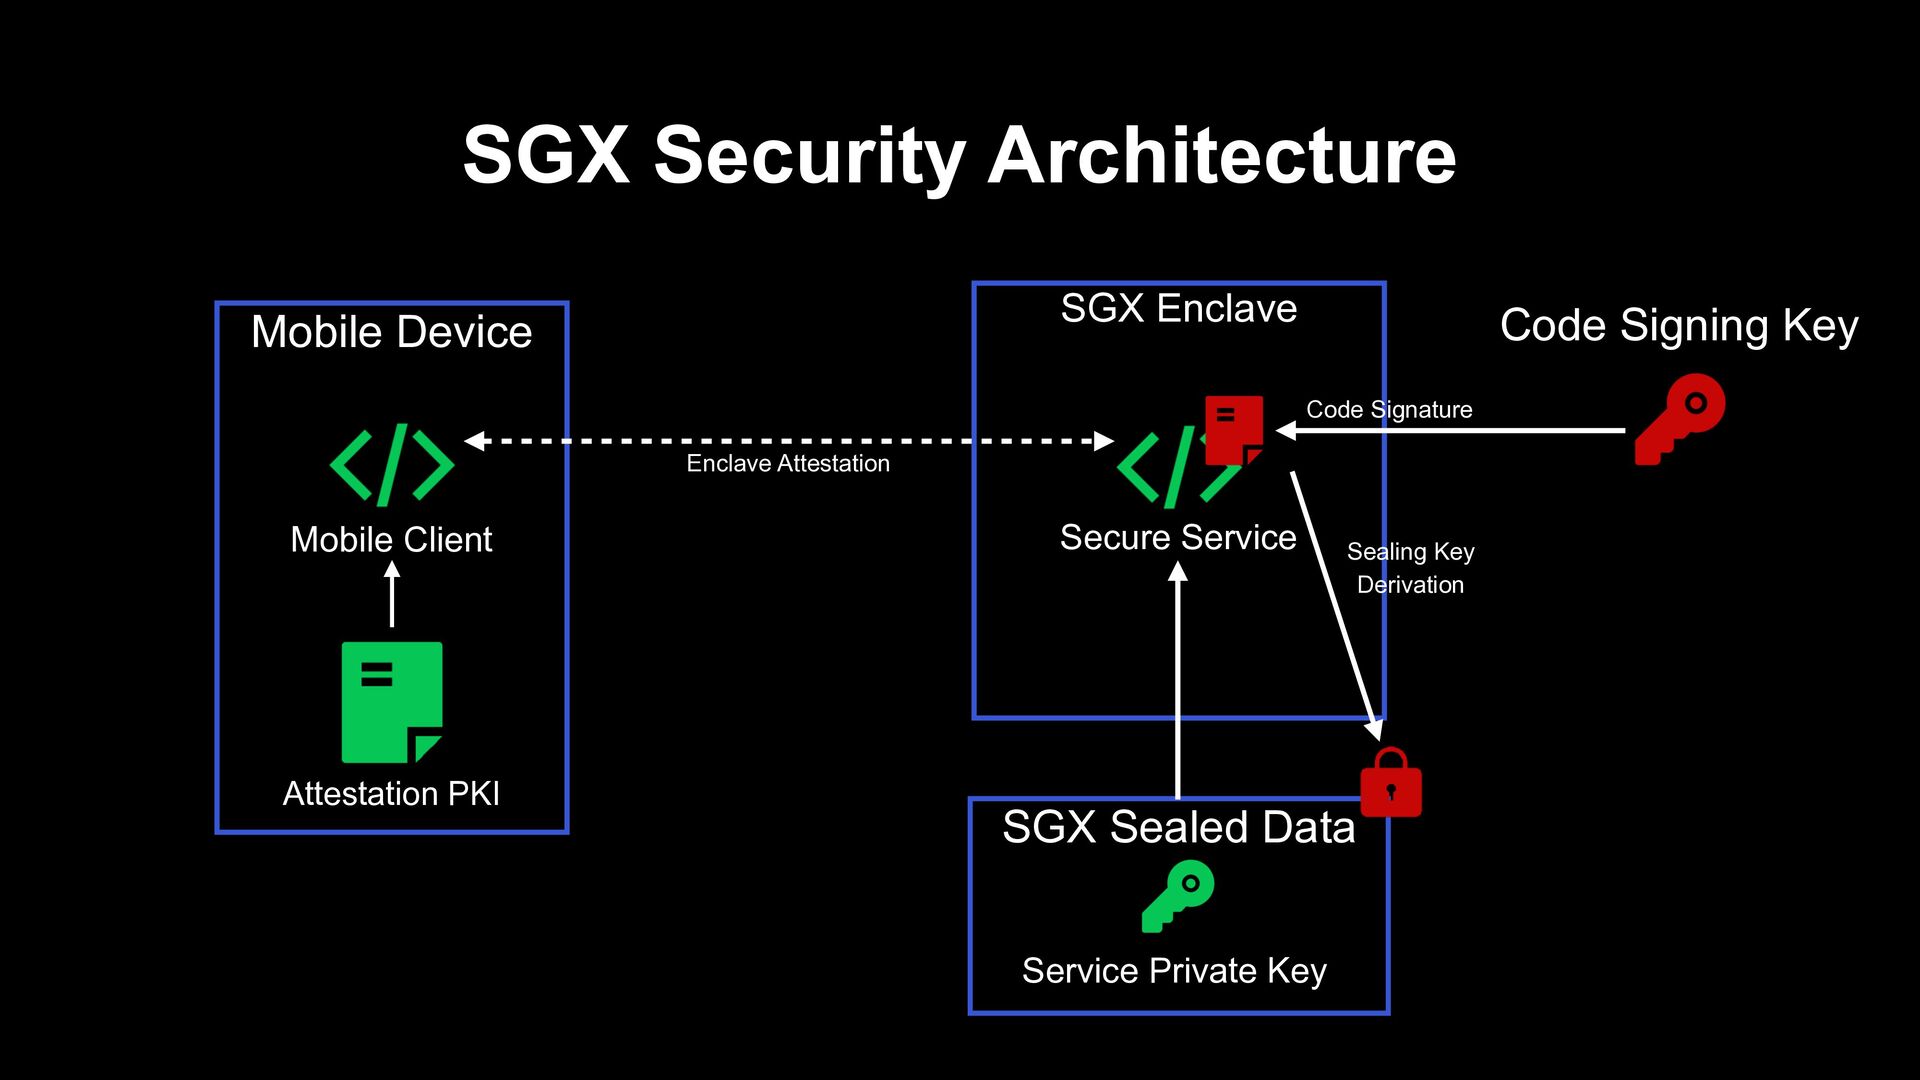
SGX Security Architecture Mobile Device Attestation PKI SGX Enclave Secure
Service SGX Sealed Data Service Private Key Code Signing Key Code Signature Enclave Attestation Sealing Key Derivation Mobile Client -
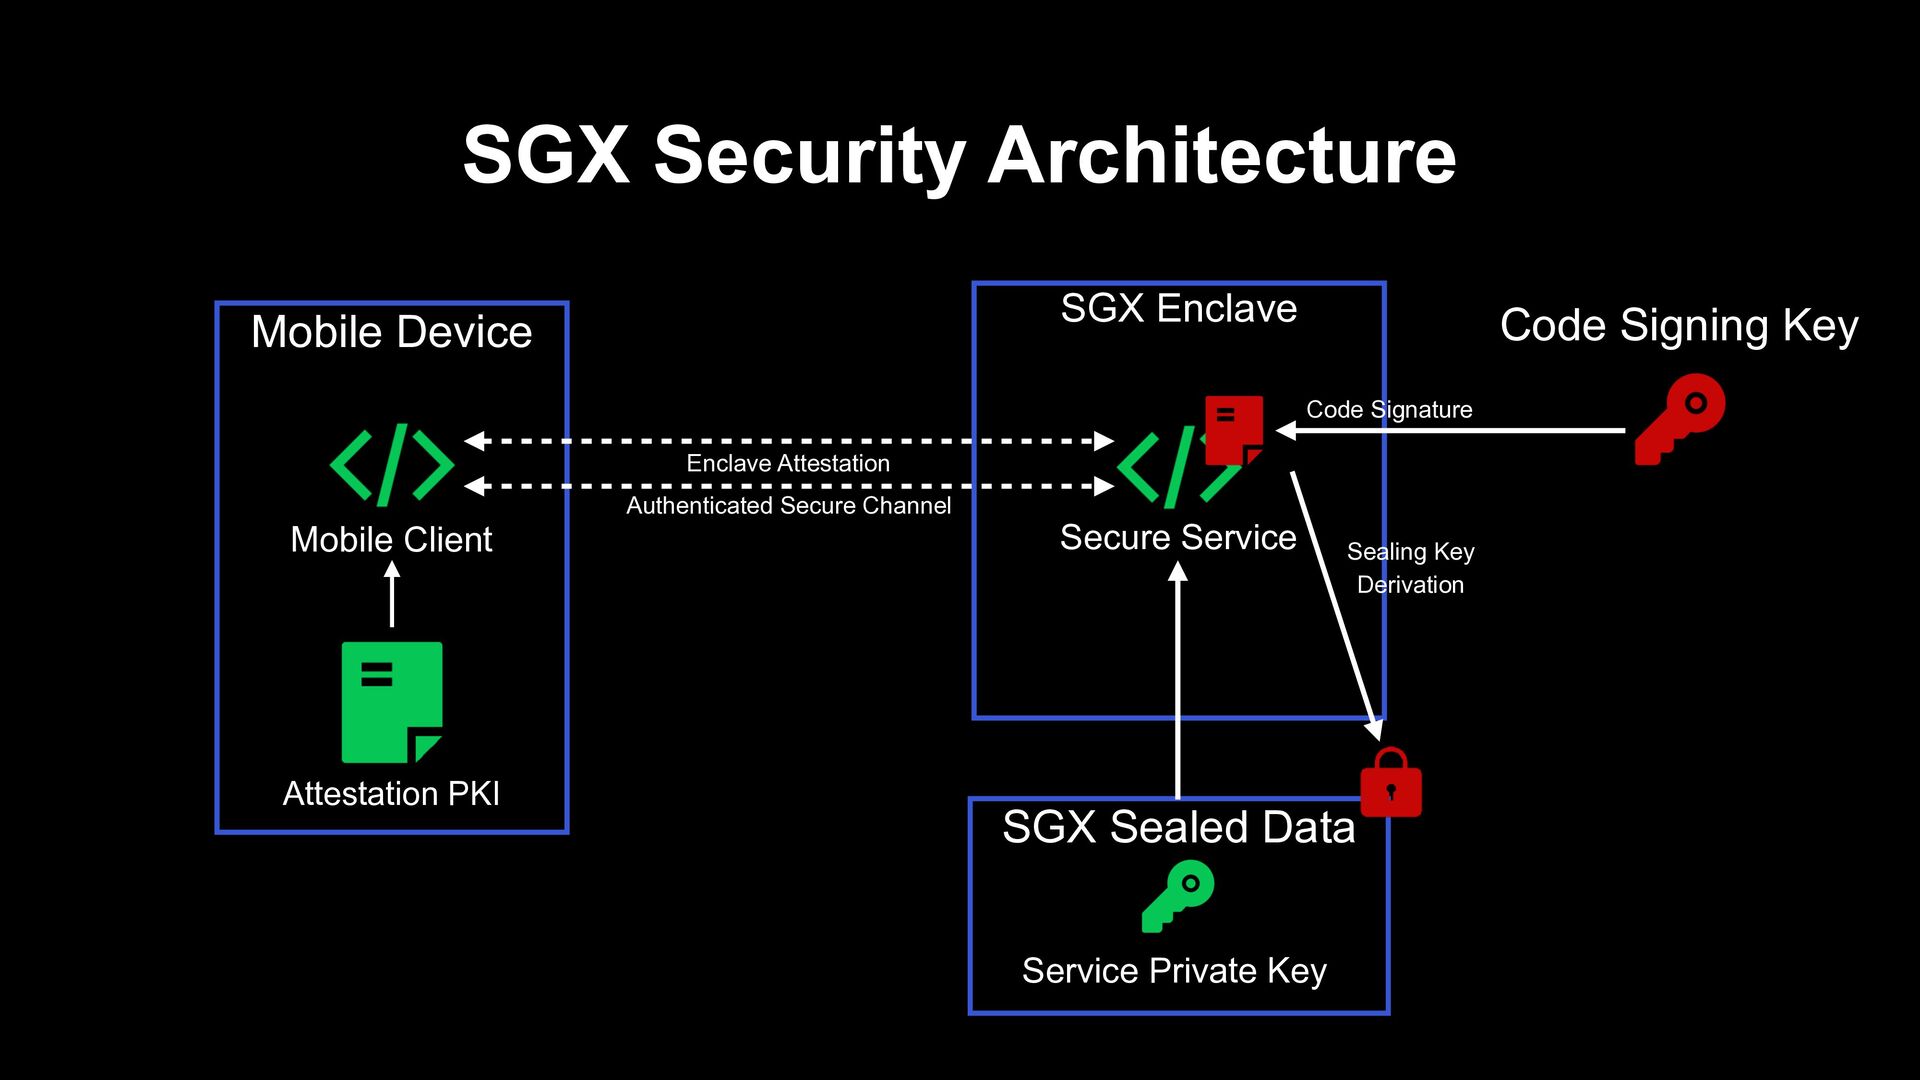
SGX Security Architecture Mobile Device Attestation PKI SGX Enclave Secure
Service SGX Sealed Data Service Private Key Code Signing Key Code Signature Enclave Attestation Sealing Key Derivation Authenticated Secure Channel Mobile Client -
Are We More Secure? - Reduce the attack surface -
Trusted Computing Base: -
Are We More Secure? - Reduce the attack surface -
Trusted Computing Base: Sum of components critical to security -
Are We More Secure? - Reduce the attack surface -
Trusted Computing Base: Sum of components critical to security - No need to trust the OS / user applications -
Are We More Secure? - Reduce the attack surface -
Trusted Computing Base: Sum of components critical to security - No need to trust the OS / user applications - Move security functions into hardware -
Are We More Secure? - Reduce the attack surface -
Trusted Computing Base: Sum of components critical to security - No need to trust the OS / user applications - Move security functions into hardware - Hardware attack cost is much higher -
TCB Threats - Hardware vulnerabilities - Recent examples: ÆPIC leak,
SEPROM bug, … - Cryptographic vulnerabilities -
TCB Threats - Hardware vulnerabilities - Recent examples: ÆPIC leak,
SEPROM bug, … - Cryptographic vulnerabilities - Side channel attacks -
TCB Threats - Hardware vulnerabilities - Recent examples: ÆPIC leak,
SEPROM bug, … - Cryptographic vulnerabilities - Side channel attacks - Insecure protocol design -
TCB Threats - Hardware vulnerabilities - Recent examples: ÆPIC leak,
SEPROM bug, … - Cryptographic vulnerabilities - Side channel attacks - Insecure protocol design - Memory vulnerabilities -
TCB Threats - Hardware vulnerabilities - Recent examples: ÆPIC leak,
SEPROM bug, … - Cryptographic vulnerabilities - Side channel attacks - Insecure protocol design - Memory vulnerabilities - Memory leaks -
TCB Threats - Hardware vulnerabilities - Recent examples: ÆPIC leak,
SEPROM bug, … - Cryptographic vulnerabilities - Side channel attacks - Insecure protocol design - Memory vulnerabilities - Memory leaks - Arbitrary code execution -
TCB Threats - Hardware vulnerabilities - Recent examples: ÆPIC leak,
SEPROM bug, … - Cryptographic vulnerabilities - Side channel attacks - Insecure protocol design - Memory vulnerabilities - Memory leaks - Arbitrary code execution Affect all TEEs, Can only mitigate -
Back To Secure Development - Cryptographic protocol design flaws -
Formal verification can help: proverif -
Back To Secure Development - Cryptographic protocol design flaws -
Formal verification can help: proverif - Memory vulnerabilities -
Back To Secure Development - Cryptographic protocol design flaws -
Formal verification can help: proverif - Memory vulnerabilities - Testing and Fuzzing helps -
Back To Secure Development - Cryptographic protocol design flaws -
Formal verification can help: proverif - Memory vulnerabilities - Testing and Fuzzing helps - Safer languages are better: Rust -
Rust - Higher level abstraction than C - Rich type
system - Advanced generic programming -
Rust - Higher level abstraction than C - Rich type
system - Advanced generic programming - Crates: module based dependency management -
Rust - Higher level abstraction than C - Rich type
system - Advanced generic programming - Crates: module based dependency management - Designed with security in mind -
Rust - Higher level abstraction than C - Rich type
system - Advanced generic programming - Crates: module based dependency management - Designed with security in mind - Compiler enforce memory safety, thread safety -
Rust - Higher level abstraction than C - Rich type
system - Advanced generic programming - Crates: module based dependency management - Designed with security in mind - Compiler enforce memory safety, thread safety - Native with bare metal support -
Rust - Higher level abstraction than C - Rich type
system - Advanced generic programming - Crates: module based dependency management - Designed with security in mind - Compiler enforce memory safety, thread safety - Native with bare metal support - Can be as fast as C -
Rust - Higher level abstraction than C - Rich type
system - Advanced generic programming - Crates: module based dependency management - Designed with security in mind - Compiler enforce memory safety, thread safety - Native with bare metal support - Can be as fast as C - Can be used to write firmware, drivers, SGX enclave, … -
Rust at LINE - Currently only using it on the
server application side -
Rust at LINE - Currently only using it on the
server application side - Excellent ecosystem for service development -
Rust at LINE - Currently only using it on the
server application side - Excellent ecosystem for service development - Started using it for SGX enclave -
Rust at LINE - Currently only using it on the
server application side - Excellent ecosystem for service development - Started using it for SGX enclave - Toolchains already exists: Apache Teaclave, Fortanix® EDP -
Rust at LINE - Currently only using it on the
server application side - Excellent ecosystem for service development - Started using it for SGX enclave - Toolchains already exists: Apache Teaclave, Fortanix® EDP - Easy to make your own -
Rust at LINE - Currently only using it on the
server application side - Excellent ecosystem for service development - Started using it for SGX enclave - Toolchains already exists: Apache Teaclave, Fortanix® EDP - Easy to make your own - Rust can output C compatible (FFI) object files -
Rust at LINE - Currently only using it on the
server application side - Excellent ecosystem for service development - Started using it for SGX enclave - Toolchains already exists: Apache Teaclave, Fortanix® EDP - Easy to make your own - Rust can output C compatible (FFI) object files - Rust nostd code can be linked with Intel SDK -
Conclusions - Higher security assurance can be achieved on the
server side - TEE can help prevent insider threats -
Conclusions - Higher security assurance can be achieved on the
server side - TEE can help prevent insider threats - TEE can protect both data and code -
Conclusions - Higher security assurance can be achieved on the
server side - TEE can help prevent insider threats - TEE can protect both data and code - Multiple TEE implementation available -
Conclusions - Higher security assurance can be achieved on the
server side - TEE can help prevent insider threats - TEE can protect both data and code - Multiple TEE implementation available - Similar security architecture can be achieved -
Conclusions - Higher security assurance can be achieved on the
server side - TEE can help prevent insider threats - TEE can protect both data and code - Multiple TEE implementation available - Similar security architecture can be achieved - Choice will depend on cost, performance, regulations, … -
Conclusions - Higher security assurance can be achieved on the
server side - TEE can help prevent insider threats - TEE can protect both data and code - Multiple TEE implementation available - Similar security architecture can be achieved - Choice will depend on cost, performance, regulations, … - TEE TCB is still a target -
Conclusions - Higher security assurance can be achieved on the
server side - TEE can help prevent insider threats - TEE can protect both data and code - Multiple TEE implementation available - Similar security architecture can be achieved - Choice will depend on cost, performance, regulations, … - TEE TCB is still a target - Safer programming languages are required