Share
Embed
Reducing the Cost of Security in the Cloud
ACM Cloud Computing Security Workshop (CCSW), November 2014, Keynote. http://dl.acm.org/citation.cfm?id=2664184
Bryan Payne
November 07, 2014
Transcript
37 slides
-
© 2014 Nebula, Inc. All rights reserved. (cloud) Computing for
the Enterprise Reducing the Cost of Security in the Cloud Bryan D. Payne [email protected] -
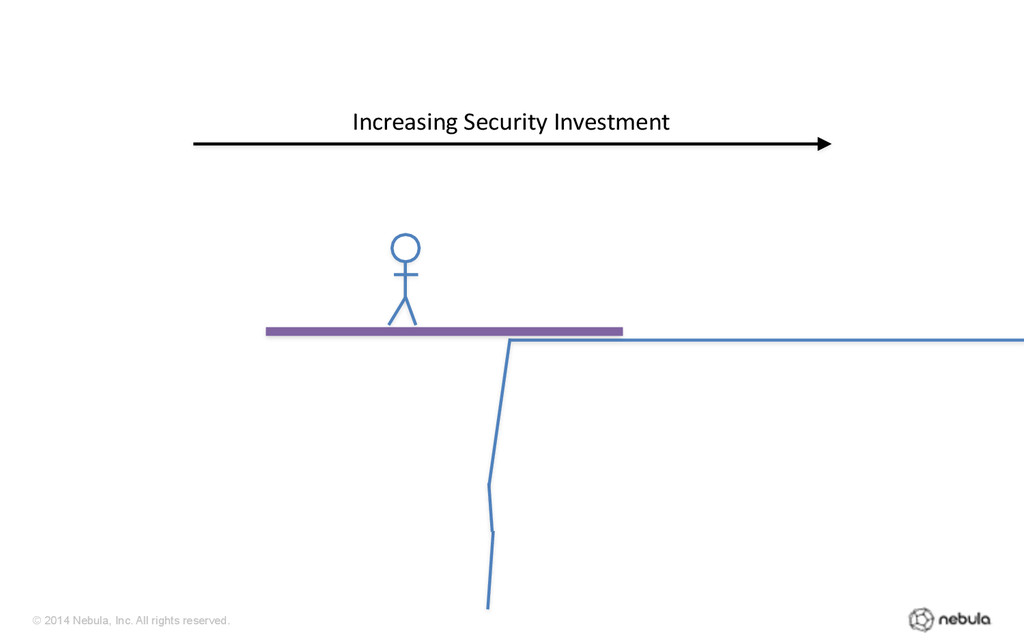
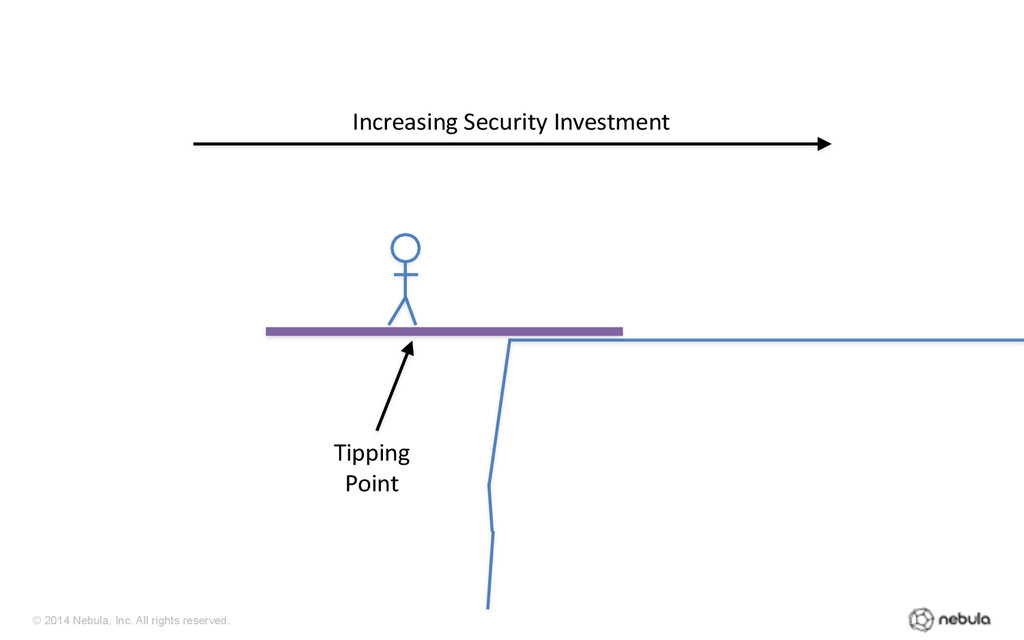
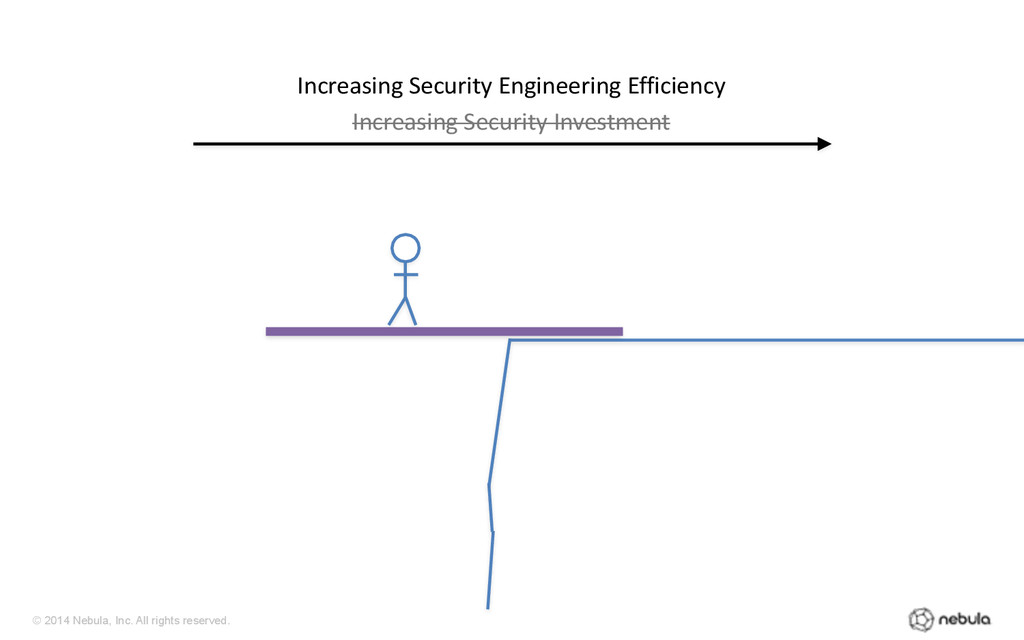
© 2014 Nebula, Inc. All rights reserved. Increasing Security Investment
Increasing Security Engineering Efficiency -
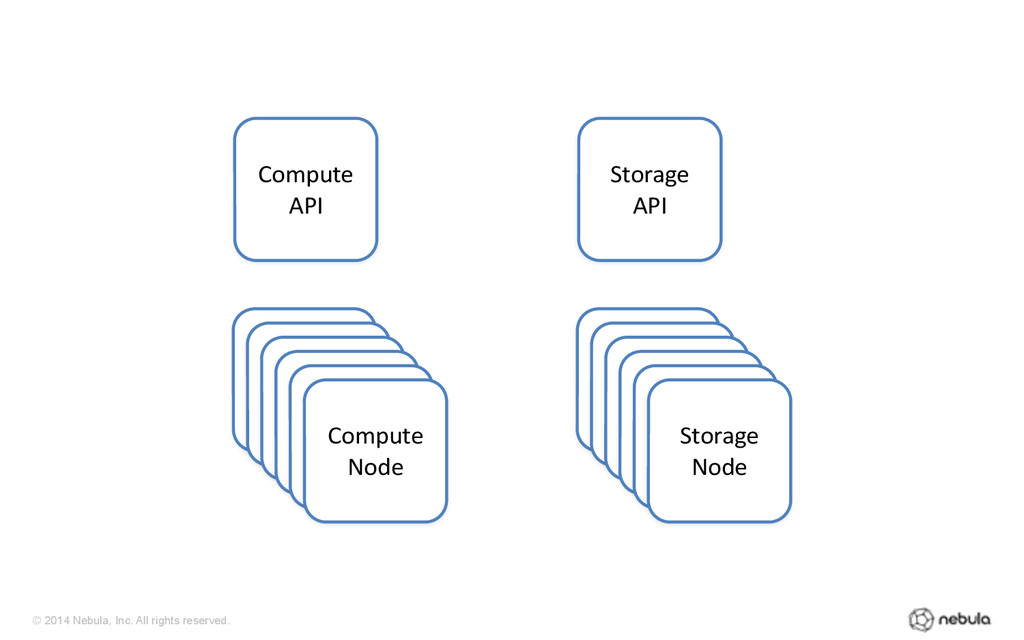
© 2014 Nebula, Inc. All rights reserved. Compute API
Compute Worker Compute Worker Compute Worker Compute Worker Compute Worker Compute Node Storage API Storage Node Storage Node Storage Node Storage Node Storage Node Storage Node -
© 2014 Nebula, Inc. All rights reserved. Storage API
Storage Node Storage Node Storage Node Storage Node Storage Node Storage Node Storage API Storage API Compute API Compute Worker Compute Worker Compute Worker Compute Worker Compute Worker Compute Node Compute API Compute API Proxy Proxy -
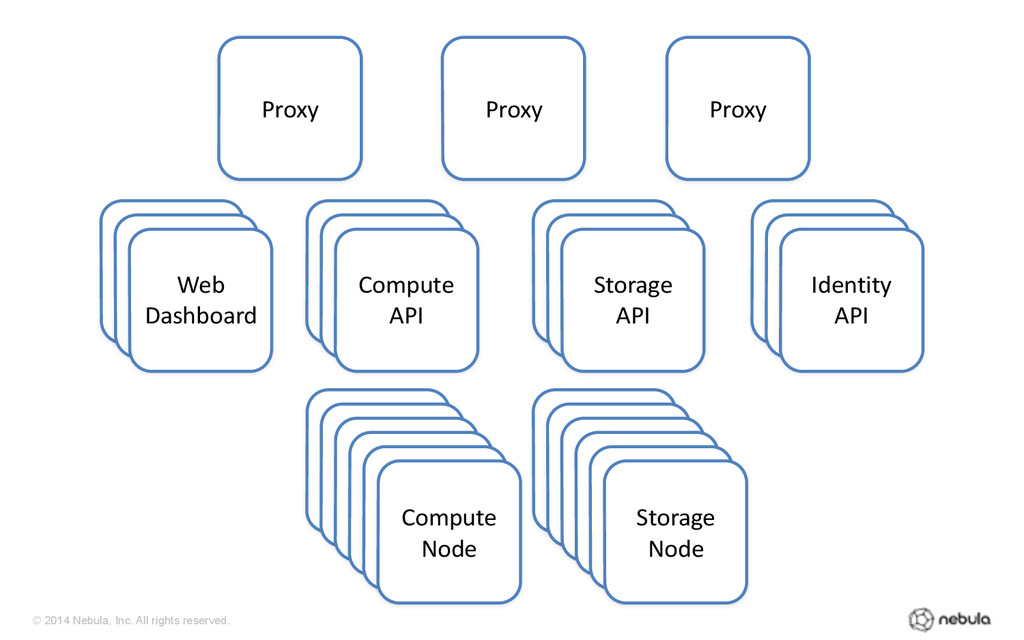
© 2014 Nebula, Inc. All rights reserved. Storage Node
Storage Node Storage Node Storage Node Storage Node Storage Node Storage API Storage API Storage API Compute Worker Compute Worker Compute Worker Compute Worker Compute Worker Compute Node Compute API Compute API Compute API Proxy Proxy Storage API Storage API Identity API Storage API Storage API Web Dashboard Proxy -
© 2014 Nebula, Inc. All rights reserved. Storage Node
Storage Node Storage Node Storage Node Storage Node Storage Node Compute Worker Compute Worker Compute Worker Compute Worker Compute Worker Compute Node Proxy Proxy Storage API Storage API Identity API Storage API Storage API Web Dashboard Proxy Message Bus Rest APIs Compute API Compute API Compute API Storage API Storage API Storage API -
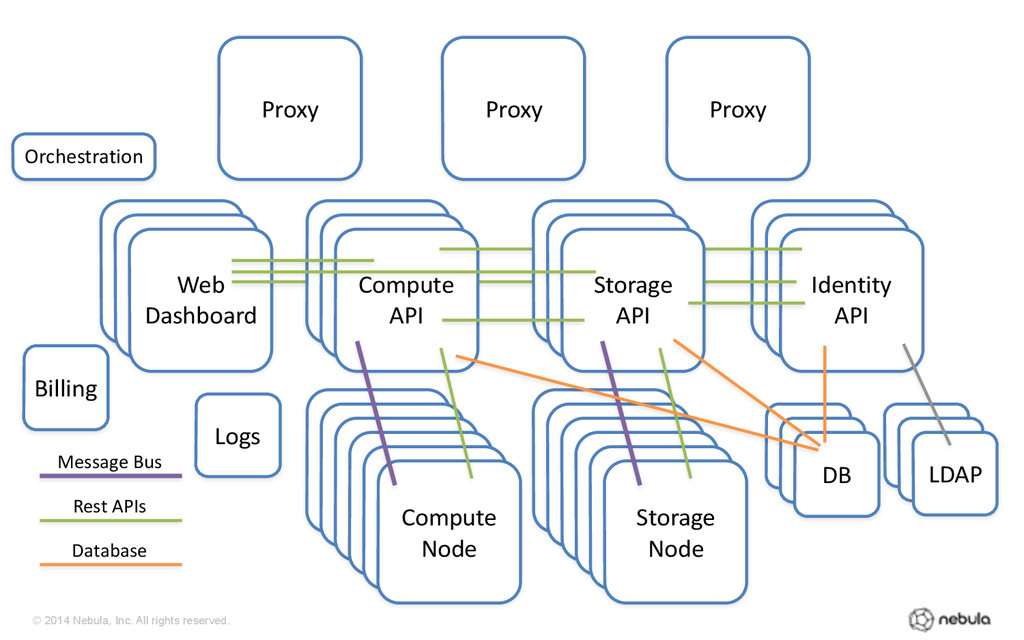
© 2014 Nebula, Inc. All rights reserved. Storage Node
Storage Node Storage Node Storage Node Storage Node Storage Node Compute Worker Compute Worker Compute Worker Compute Worker Compute Worker Compute Node Proxy Proxy Storage API Storage API Identity API Storage API Storage API Web Dashboard Proxy Message Bus Rest APIs Compute API Compute API Compute API Storage API Storage API Storage API Database DB DB DB LDAP LDAP LDAP Logs Billing Orchestration -
© 2014 Nebula, Inc. All rights reserved. Storage Node
Storage Node Storage Node Storage Node Storage Node Storage Node Compute Worker Compute Worker Compute Worker Compute Worker Compute Worker Compute Node Proxy Proxy Storage API Storage API Identity API Storage API Storage API Web Dashboard Proxy Message Bus Rest APIs Compute API Compute API Compute API Storage API Storage API Storage API Database DB DB DB LDAP LDAP LDAP Logs CA Secret Mgmt Billing Orchestration Sec Policy -
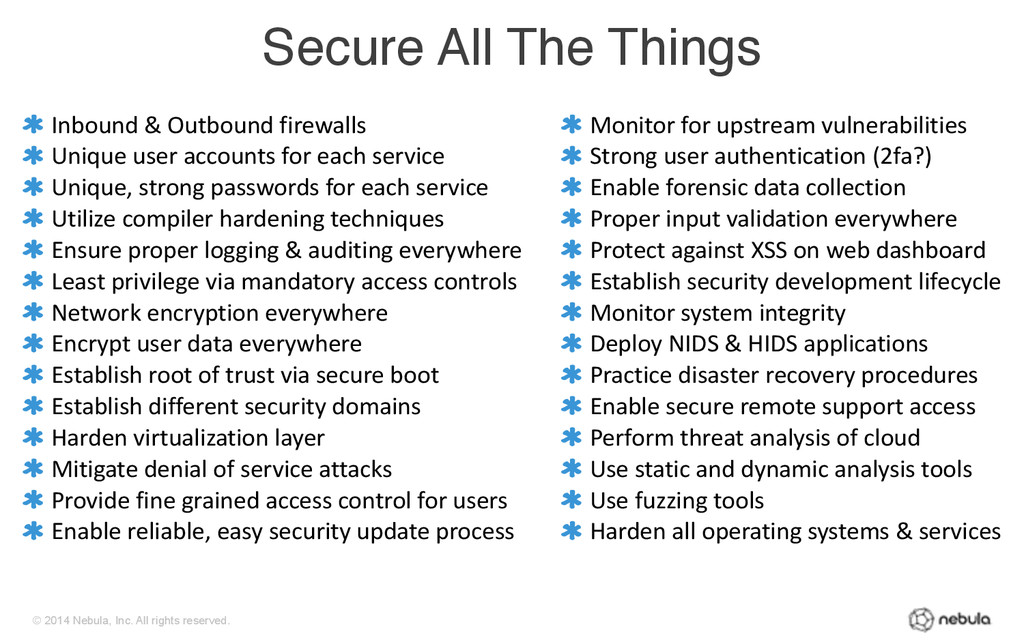
© 2014 Nebula, Inc. All rights reserved. Secure All The
Things Inbound & Outbound firewalls Unique user accounts for each service Unique, strong passwords for each service Utilize compiler hardening techniques Ensure proper logging & auditing everywhere Least privilege via mandatory access controls Network encryption everywhere Encrypt user data everywhere Establish root of trust via secure boot Establish different security domains Harden virtualization layer Mitigate denial of service attacks Provide fine grained access control for users Enable reliable, easy security update process Monitor for upstream vulnerabilities Strong user authentication (2fa?) Enable forensic data collection Proper input validation everywhere Protect against XSS on web dashboard Establish security development lifecycle Monitor system integrity Deploy NIDS & HIDS applications Practice disaster recovery procedures Enable secure remote support access Perform threat analysis of cloud Use static and dynamic analysis tools Use fuzzing tools Harden all operating systems & services -
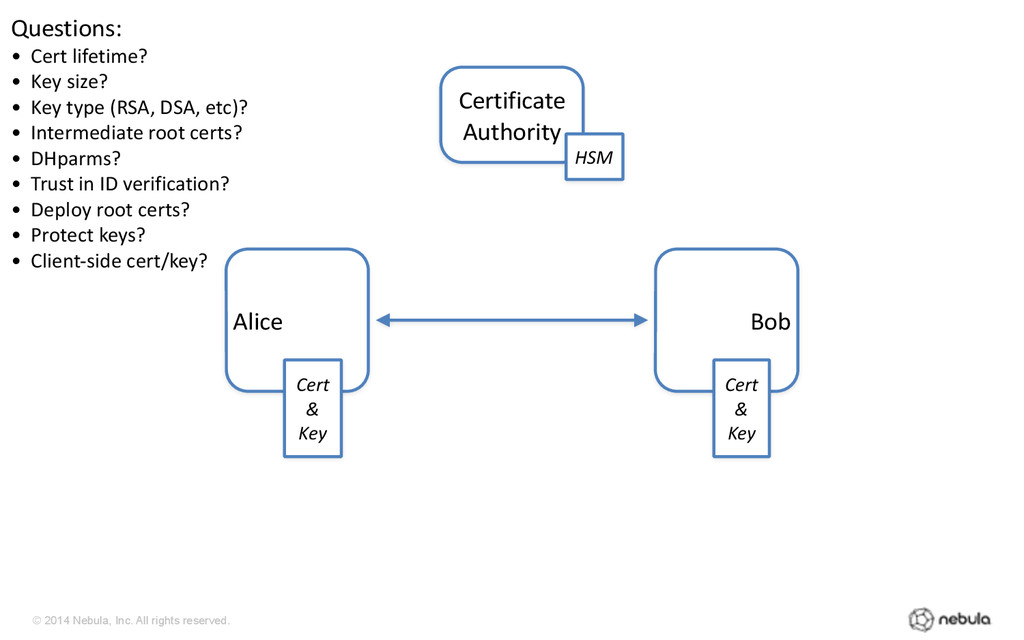
© 2014 Nebula, Inc. All rights reserved. Alice Bob Cert
& Key Cert & Key Certificate Authority Questions: • Cert lifetime? • Key size? • Key type (RSA, DSA, etc)? • Intermediate root certs? • DHparms? • Trust in ID verification? • Deploy root certs? • Protect keys? • Client-‐side cert/key? HSM -
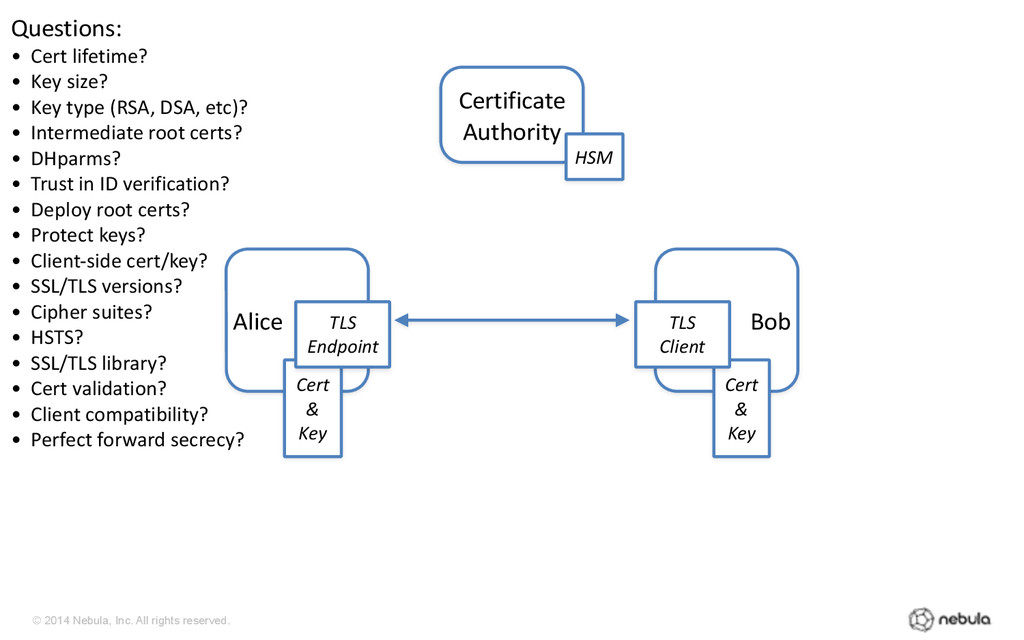
© 2014 Nebula, Inc. All rights reserved. Alice Bob Cert
& Key Cert & Key Certificate Authority Questions: • Cert lifetime? • Key size? • Key type (RSA, DSA, etc)? • Intermediate root certs? • DHparms? • Trust in ID verification? • Deploy root certs? • Protect keys? • Client-‐side cert/key? • SSL/TLS versions? • Cipher suites? • HSTS? • SSL/TLS library? • Cert validation? • Client compatibility? • Perfect forward secrecy? TLS Endpoint TLS Client HSM -
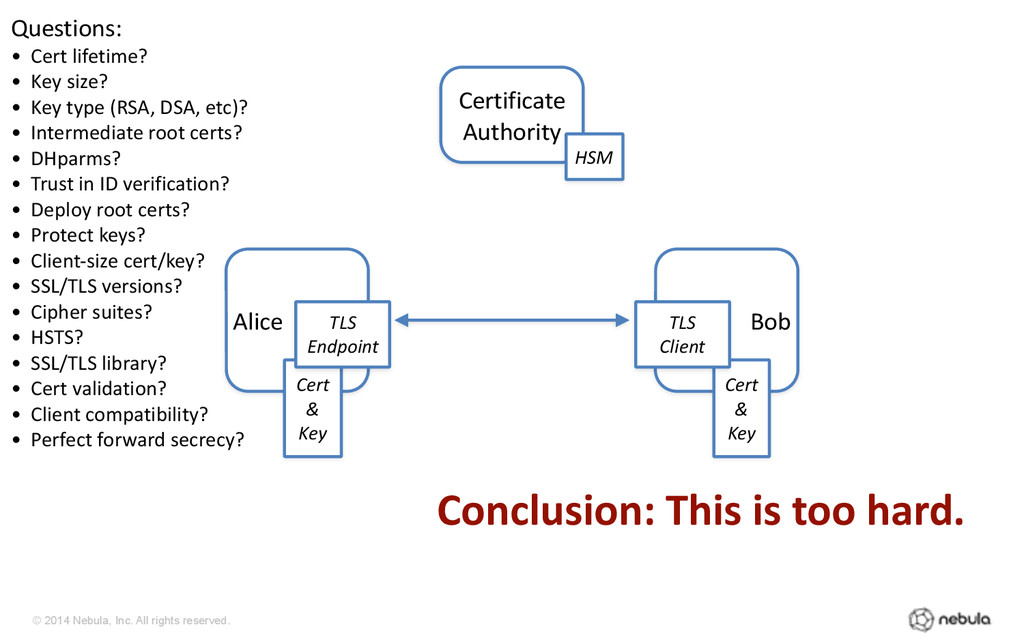
© 2014 Nebula, Inc. All rights reserved. Alice Bob Cert
& Key Cert & Key Certificate Authority Questions: • Cert lifetime? • Key size? • Key type (RSA, DSA, etc)? • Intermediate root certs? • DHparms? • Trust in ID verification? • Deploy root certs? • Protect keys? • Client-‐size cert/key? • SSL/TLS versions? • Cipher suites? • HSTS? • SSL/TLS library? • Cert validation? • Client compatibility? • Perfect forward secrecy? TLS Endpoint TLS Client HSM Conclusion: This is too hard. -
© 2014 Nebula, Inc. All rights reserved. Key Security Primitives
Protect Network Communications Protect Data at Rest Generate, Store, and Use Secrets Authentication & Authorization -
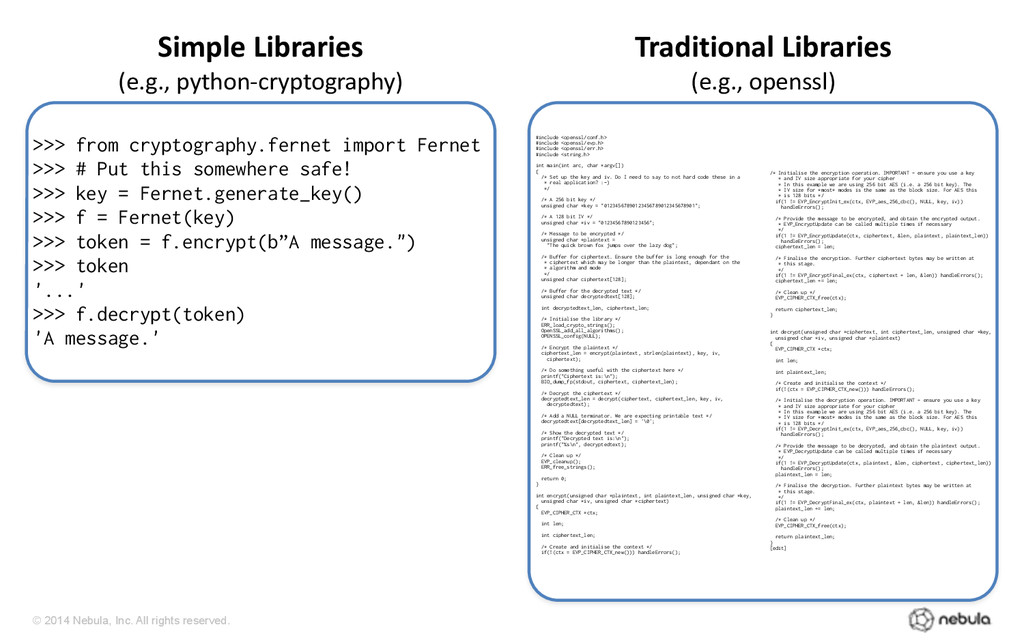
© 2014 Nebula, Inc. All rights reserved. >>> from cryptography.fernet
import Fernet >>> # Put this somewhere safe! >>> key = Fernet.generate_key() >>> f = Fernet(key) >>> token = f.encrypt(b”A message.") >>> token '...' >>> f.decrypt(token) 'A message.' Simple Libraries (e.g., python-‐cryptography) #include <openssl/conf.h> #include <openssl/evp.h> #include <openssl/err.h> #include <string.h> int main(int arc, char *argv[]) { /* Set up the key and iv. Do I need to say to not hard code these in a * real application? :-) */ /* A 256 bit key */ unsigned char *key = "01234567890123456789012345678901"; /* A 128 bit IV */ unsigned char *iv = "01234567890123456"; /* Message to be encrypted */ unsigned char *plaintext = "The quick brown fox jumps over the lazy dog"; /* Buffer for ciphertext. Ensure the buffer is long enough for the * ciphertext which may be longer than the plaintext, dependant on the * algorithm and mode */ unsigned char ciphertext[128]; /* Buffer for the decrypted text */ unsigned char decryptedtext[128]; int decryptedtext_len, ciphertext_len; /* Initialise the library */ ERR_load_crypto_strings(); OpenSSL_add_all_algorithms(); OPENSSL_config(NULL); /* Encrypt the plaintext */ ciphertext_len = encrypt(plaintext, strlen(plaintext), key, iv, ciphertext); /* Do something useful with the ciphertext here */ printf("Ciphertext is:\n"); BIO_dump_fp(stdout, ciphertext, ciphertext_len); /* Decrypt the ciphertext */ decryptedtext_len = decrypt(ciphertext, ciphertext_len, key, iv, decryptedtext); /* Add a NULL terminator. We are expecting printable text */ decryptedtext[decryptedtext_len] = '\0'; /* Show the decrypted text */ printf("Decrypted text is:\n"); printf("%s\n", decryptedtext); /* Clean up */ EVP_cleanup(); ERR_free_strings(); return 0; } int encrypt(unsigned char *plaintext, int plaintext_len, unsigned char *key, unsigned char *iv, unsigned char *ciphertext) { EVP_CIPHER_CTX *ctx; int len; int ciphertext_len; /* Create and initialise the context */ if(!(ctx = EVP_CIPHER_CTX_new())) handleErrors(); Traditional Libraries (e.g., openssl) /* Initialise the encryption operation. IMPORTANT - ensure you use a key * and IV size appropriate for your cipher * In this example we are using 256 bit AES (i.e. a 256 bit key). The * IV size for *most* modes is the same as the block size. For AES this * is 128 bits */ if(1 != EVP_EncryptInit_ex(ctx, EVP_aes_256_cbc(), NULL, key, iv)) handleErrors(); /* Provide the message to be encrypted, and obtain the encrypted output. * EVP_EncryptUpdate can be called multiple times if necessary */ if(1 != EVP_EncryptUpdate(ctx, ciphertext, &len, plaintext, plaintext_len)) handleErrors(); ciphertext_len = len; /* Finalise the encryption. Further ciphertext bytes may be written at * this stage. */ if(1 != EVP_EncryptFinal_ex(ctx, ciphertext + len, &len)) handleErrors(); ciphertext_len += len; /* Clean up */ EVP_CIPHER_CTX_free(ctx); return ciphertext_len; } int decrypt(unsigned char *ciphertext, int ciphertext_len, unsigned char *key, unsigned char *iv, unsigned char *plaintext) { EVP_CIPHER_CTX *ctx; int len; int plaintext_len; /* Create and initialise the context */ if(!(ctx = EVP_CIPHER_CTX_new())) handleErrors(); /* Initialise the decryption operation. IMPORTANT - ensure you use a key * and IV size appropriate for your cipher * In this example we are using 256 bit AES (i.e. a 256 bit key). The * IV size for *most* modes is the same as the block size. For AES this * is 128 bits */ if(1 != EVP_DecryptInit_ex(ctx, EVP_aes_256_cbc(), NULL, key, iv)) handleErrors(); /* Provide the message to be decrypted, and obtain the plaintext output. * EVP_DecryptUpdate can be called multiple times if necessary */ if(1 != EVP_DecryptUpdate(ctx, plaintext, &len, ciphertext, ciphertext_len)) handleErrors(); plaintext_len = len; /* Finalise the decryption. Further plaintext bytes may be written at * this stage. */ if(1 != EVP_DecryptFinal_ex(ctx, plaintext + len, &len)) handleErrors(); plaintext_len += len; /* Clean up */ EVP_CIPHER_CTX_free(ctx); return plaintext_len; } [edit] -
© 2014 Nebula, Inc. All rights reserved. Identify the correct
security infrastructure primitives, and make them broadly usable. Create high quality modern software libraries for these primitives. Ensure that today’s (and tomorrow’s!) software building blocks create secure applications automatically. -
© 2014 Nebula, Inc. All rights reserved. (cloud) Computing for
the Enterprise Reducing the Cost of Security in the Cloud Bryan D. Payne [email protected]