Share
Embed
JSON Web Token Authentication for Mobile Application
社内説明用資料
Transcript
33 slides
-
Agenda • JSON Web Token (JWT) • OAuth 2.0 JWT
Bearer Token Profile • OAuth 2.0 Client Authentication for Mobile Application • Certificate Pinning -
JSON Web Token (JWT) ! • HTTP HeaderΫΤϦύϥϝʔλͷΑ͏ͳαΠζʹ੍ݶ͕͋ΔྖҬͰ༻ ͞ΕΔ͜ͱΛҙਤͨ͠ίϯύΫτͳΫϨʔϜදݱϑΥʔϚοτ •
JSONΦϒδΣΫτ(จࣈྻ)ʹΤϯίʔυ͢Δ • ӳ୯ޠͷ”jot”ͱಉ͡ൃԻ͕ਪ͞Ε͍ͯΔ • Google, Salesforce, Yahoo JapanͰ࠾༻ -
JWE / JWS • ϖΠϩʔυͱͯ͠JWE/JWSͷ2͕ͭ͋ΓɺͦΕͧΕ༷ͱׂͯ͠͞Εͨ • JSON Web Encryption (JWE):
ίϯςϯτͷ҉߸ԽΛߦ͏ • JSON Web Segnature (JWS): ίϯςϯτͷॺ໊Λߦ͏ ! • ༻ࣄྫ͕ଟ͍ͷJWS • OAuth 2.0 / OpenID Connect -
The structure of JWT(JWS) • ϔομ+ϖΠϩʔυ+γάωνϟͷ3ͭͰߏ • BASE64URLΤϯίʔυͨ͠จࣈྻΛ”.”Ͱ࿈݁ͨ͠จࣈྻͱͯ͠දݱ͞ΕΔ { "typ":"JWT",
"alg":"HS256" } { "iss":"JWT", "sub":"HS256", "exp":1412735596,... } BASE64URL(HMACSHA256( BASE64URL(header) + "." + BASE64URL(payload), "shared_key")) Header Payload Signature ewogICJ0eXAiOiJKV1QiLAogICJh bGciOiJIUzI1NiIKfQo ewogICJpc3MiOiJKV1QiLAogICJz dWIiOiJIUzI1NiIsCiAgImV4cCI6 MTQxMjczNTU5NiwuLi4KfQo NWYzOGY0NmYwYjlkYWY3Mjc0OGI3 MWVlNzRhMDRlMGM2ZDlkNzVmNmZk OWJmMGM3ZTViYmE3MjU3OTY4MThj ZQo BASE64 URL ENCODED ewogICJ0eXAiOiJKV1QiLAogICJhbGciO iJIUzI1NiIKfQo.ewogICJpc3MiOiJKV1 QiLAogICJzdWIiOiJIUzI1NiIsCiAgImV 4cCI6MTQxMjczNTU5NiwuLi4KfQo.NWYz OGY0NmYwYjlkYWY3Mjc0OGI3MWVlNzRhM DRlMGM2ZDlkNzVmNmZkOWJmMGM3ZTViYm E3MjU3OTY4MThjZQo concat JSON Web Token -
JWT Header • ΄ͱΜͲͷύϥϝʔλOPTIONALɹ (JWSͷඞਢύϥϝʔλ1ͭ) • ໊લۭؒJWTɺJWEɺJWSͷ༷Ͱڞ༗͞Ε͍ͯΔ • ϔομۭؒͷύϥϝʔλࣗ༝ʹՃͯ͠ྑ͍ {"typ":"JWT",
"alg":"HS256"} "JWT"·ͨ"urn:ietf:params:oauth:token-type:jwt" ॺ໊ΞϧΰϦζϜ (REQUIRED) -
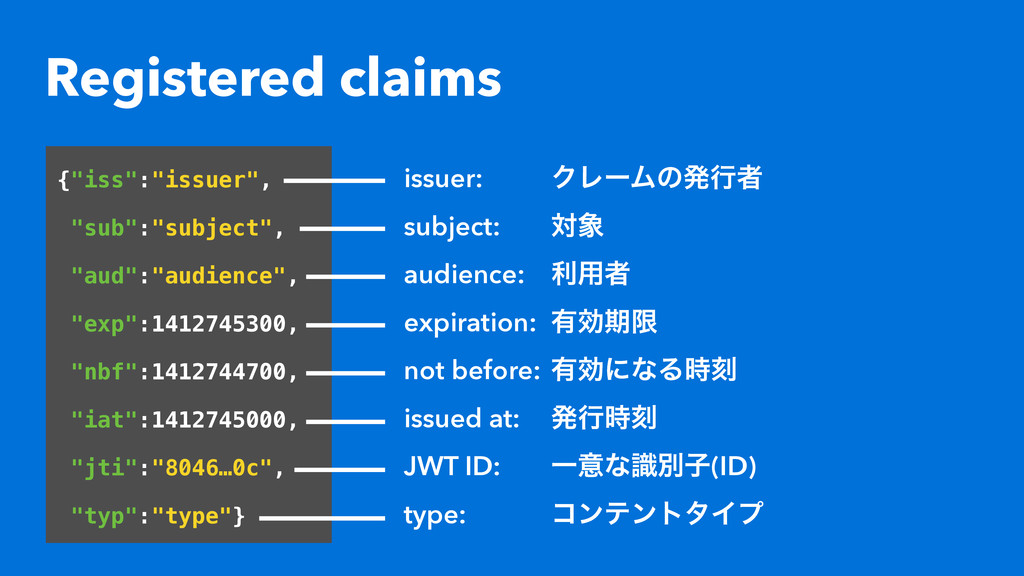
Registered claims {"iss":"issuer", "sub":"subject", "aud":"audience", "exp":1412745300, "nbf":1412744700, "iat":1412745000, "jti":"8046…0c", "typ":"type"}
issuer: ΫϨʔϜͷൃߦऀ subject: ର audience: ར༻ऀ expiration: ༗ޮظݶ not before: ༗ޮʹͳΔ࣌ࠁ issued at: ൃߦ࣌ࠁ JWT ID: Ұҙͳࣝผࢠ(ID) type: ίϯςϯτλΠϓ -
Signature • ϔομͱϖΠϩʔυΛBASE64URLΤϯίʔυͯ͠ɺ"."Ͱ࿈݁ͨ͠จࣈྻͷ ॺ໊Λܭࢉ͠ɺBASE64URLΤϯίʔυͨ͠ͷ • ΞϧΰϦζϜ͕HS256(HMAC SHA-256)ͷ߹࣍ͷΑ͏ʹͳΔ BASE64URL( HMACSHA256( BASE64URL(header)
+ "." + BASE64URL(payload), "shared_key" ) ) -
Signature algorithm alg Digital Signature / MAC Algorithm Requirements HS256
HMAC using SHA-256 Required HS384 HMAC using SHA-384 Optional HS512 HMAC using SHA-512 Optional RS256 RSASSA-PKCS-v1.5 using SHA-256 Recommended RS384 RSASSA-PKCS-v1.5 using SHA-384 Optional RS512 RSASSA-PKCS-v1.5 using SHA-512 Optional ES256 ECDSA using P-256 and SHA-256 Recommended+ ES512 ECDSA using P-384 and SHA-384 Optional PS256 RSASSA-PSS using SHA-256 and MGF1 with SHA-256 Optional PS384 RSASSA-PSS using SHA-384 and MGF1 with SHA-384 Optional PS512 RSASSA-PSS using SHA-512 and MGF1 with SHA-512 Optional -
OAuth 2.0 JWT Bearer token profile • JWTʹΑΓΞΫηετʔΫϯΛཁٻ͢ΔOAuth2.0ͷ֦ு༷ • JWTΛ༻͍ͯGrant
AuthorizationΛߦ͏ • JWTΛ༻͍ͯClient AuthenticationΛߦ͏ • Client AuthenticationOAuth 2.0 Assertionsͱͯ͠ඪ४Խ͕ਐΜͰ͍ Δ֦ு༷ • JWSʹΑΓॺ໊Λߦ͏ͷͰൿີ伴ɺ·ͨڞ༗伴͕࿙Ӯ͠ͳ͍ݶΓ τʔΫϯͷվ͟Μ͕͍͠ • IDΛ֬ೝ͢Δ͜ͱͰϦϓϨΠ߈ܸΛ͙͜ͱ͕ग़དྷΔ -
JWT Bearer token flow Client Authorization Server private key public
key grant_type=urn:ietf:params:oauth:grant-type:jwt-bearer assertion=(JWT token) access_token=(ACCESS TOKEN) … • JWTτʔΫϯΛ༻ͯ͠ΞΫηετʔΫϯΛऔಘ͢Δ -
JWT for grant authorisation • ϖΠϩʔυʹҎԼͷΛࢦఆ͢Δ {"iss":"issuer", "sub":"subject", "aud":"audience", "exp":1412745300,
"nbf":1412744700, "iat":1412745000, "jti":"8046…0c"} ΫϨʔϜͷൃߦऀͷUIDΛؚΊΔ ର(Ϣʔβʔ໊ϝʔϧΞυϨε) [REQUIRED] ड৴ऀ(ೝূαʔό) ༗ޮظݶ [REQUIRED] ༗ޮʹͳΔ࣌ࠁ [OPTIONAL] ൃߦ࣌ࠁ [OPTIONAL] Ұҙͳࣝผࢠ [REQUIRED] -
Grant authentication using JWT • JWTΛassertionύϥϝʔλʹࢦఆͯ͠ϦΫΤετ͢Δ • grant_type"urn:ietf:params:oauth:client-assertion-type:jwt-bearer" • αʔόॺ໊Λݕূ͠ݖݶͷaccess_tokenΛฦ͢
POST /token/oauth2 HTTP/1.1 Host: www.example.com Content-Type: application/x-www-form-urlencoded ! grant_type=urn%3Aietf%3Aparams%3Aoauth%3Agrant-type%3Ajwt-bearer &assertion=eyJhbGciOiJFUzI1NiJ9.eyJpc3Mi[…snip…].J9[…snip…]wP &scope=scope -
Client authentication in OAuth 2.0 Asserttion Framework for OAuth 2.0
Client Authentication and Authorization Grants http://tools.ietf.org/html/draft-ietf-oauth-assertions-16 • 3rd party applicationͳͲͷΫϥΠΞϯτΛೝূ͢ΔͨΊͷ༷ Relying Party Client Token Service Relying Party Client Third Party Created Assertion Self-issued Assertion Assertion Assertion -
Issuing client assertion • ҎԼͷ༰ΛؚΊΔ • Client assertionͷൃߦऀୈ3ऀͰΫϥΠΞϯτࣗͰྑ͍ {"iss":"issuer", "sub":"subject",
"aud":"audience", "exp":1412745300, "nbf":1412744700, "iat":1412745000, "jti":"8046…0c" } ΫϨʔϜͷൃߦऀͷUIDΛؚΊΔ client_id ड৴ऀ(ೝূαʔό) ༗ޮظݶ [REQUIRED] ༗ޮʹͳΔ࣌ࠁ [OPTIONAL] ൃߦ࣌ࠁ [OPTIONAL] Ұҙͳࣝผࢠ [REQUIRED] -
Client authentication using assertion • ϦΫΤετΛߦ͏ࡍʹClient AssertionΛՃ͢Δ • client_assertion_type urn:ietf:params:oauth:client-assertion-type:jwt-bearer
POST /token/oauth2 HTTP/1.1 Host: www.example.com Content-Type: application/x-www-form-urlencoded ! grant_type=authorization_code &code=37ac5695c507be6a15a093268fb7c592 &client_assertion_type=urn%3Aietf%3Aparams%3Aoauth %3Aclient-assertion-type%3Ajwt-bearer &client_assertion=PHNhbW[…snip…]ZT -
Client Authentication in Mobile App Client Server private key public
key grant_type=password &username=(user name) &password=(password) &client_assertion_type=urn%3Aietf%3Aparams %3Aoauth%3Aclient-assertion-type%3Ajwt-bearer &client_assertion=(client assertion) access_token=(ACCESS TOKEN) … 1. Issue Client Assertion 2. Password authorization with client assertion -
Issuing Client Assertion • Client AssertionϞόΠϧΞϓϦέʔγϣϯ͕ࣗൃߦ͢Δ • ΞϓϦέʔγϣϯʹॺ໊ͷͨΊͷൿີ伴ΛຒΊࠐΜͰ͓͘ { "iss":"(Mobile
App GUID)", "sub":"(client_id)", "aud":"(authorization server URI)", "exp":1412745300, "nbf":1412744700, "iat":1412745000, "jti":"(GUID)" } Client Assertion Payload -
Password Authorization with Client Authentication • ϢʔβͷݖݶೝূʹύεϫʔυೝূΛ༻͢Δ • ύεϫʔυೝূΛߦ͏ࡍʹclient assertionΛՃͯ͠ϦΫΤετ͢Δ
POST /token/oauth2 HTTP/1.1 Host: www.example.com Content-Type: application/x-www-form-urlencoded ! grant_type=password &username=username &password=password &client_assertion_type=urn%3Aietf%3Aparams%3Aoauth %3Aclient-assertion-type%3Ajwt-bearer &client_assertion=PHNhbW[…snip…]ZT -
Sniff the access token from the channels • ΫϥΠΞϯτʹෆਖ਼ͳূ໌ॻΛΠϯετʔϧ͢Εୈ3ऀ͕TLSূ໌ॻΛ ͢Γସ͑ͯ௨৴͢Δ͜ͱ͕ग़དྷΔ
Client MIM PROXY HTTPS SELF SIGNED CA CERTIFICATE Man In the Middle ATTACK SELF SIGNED CERTIFICATE HTTPS Server -
MITM attacks to sniff the access token • ௨৴༰Ϣʔβʔʹ༰қʹ࿐ఄ͢Δ •
ΦʔϓϯιʔεͷϓϩΩγͨ͘͞Μ͋ͬͯศར • ωΠςΟϒΞϓϦέʔγϣϯʹ͓͍ͯ௨৴࿏ͷൿಗੑΫϥΠΞϯτ ར༻ऀͷखʹҕͶΒΕ͍ͯΔ • ΫϥΠΞϯτར༻ऀ͕ނҙʹߦ͑؆୯ʹதؒऀ߈ܸ͕Մೳ • ͦͦୈ3ऀͰͳ͍ -
Pinning certificate and public key • TLSূ໌ॻ͕ਖ਼͍͠ͷ͔Ͳ͏͔ΫϥΠΞϯτͰݕূΛߦ͏ • αʔόূ໌ॻ·ͨCAূ໌ॻͷݕূΛߦ͏ •
ݕূʹূ໌ॻɺ·ͨެ։伴ͷϑΟϯΨʔϓϦϯτΛ͏ • ެ։伴ͷϑΟϯΨʔϓϦϯτΛ͑ূ໌ॻΛൃߦ͠ͳ͓ͯ͠ϑΟϯ ΨʔϓϦϯτΛߋ৽͢Δඞཁ͕ͳ͍ • iOSͰެ։伴ͷϑΟϯΨʔϓϦϯτΛܭࢉ͢Δͷ͕͍͠Έ͍ͨʁ -
Certificate pinning flow Client Server private key public key Obtaining
fingerprints list of certificate/public key -
Obtaining list of fingerprints • ϑΟϯΨʔϓϦϯτͷϦετதؒऀ߈ܸʹΑΓվ͟Μ͞ΕΔՄೳੑ͕͋Δ • JWTΛ༻͍ͯϑΟϯΨʔϓϦϯτ͕มߋ͞ΕΔ͜ͱΛ͙ { "iss":"(authorization
server URI)", "aud":"(client app name)", "exp":1412745300, "certs": ["624C18A73174F8E7988CB636CED6334AD8FEBC72"], "jti":"(GUID)" } -
Conclusion • OAuth 2.0ͰJWTʹΑΔGrant AuthorizationΛߦ͏ʹ OAuth 2.0 JWT Bearer token
profileΛ͏ • Client-side ApplicationͰݖݶͷڐՄҎ֎ʹΫϥΠΞϯτೝূ͕ ඞཁʹͳΔ • TLSΑΓ্ͷϨΠϠʔͰͷೝূॲཧ͕ඞཁʹͳΔ • JSONͰͷ҉߸Խ/ॺ໊JWTΛ͏ͱศར -
References • OAuth Documentation http://oauth.net/documentation/ • [RFC6749] The OAuth 2.0
Authorization Framework http://tools.ietf.org/html/rfc6749 • JSON Web Token https://tools.ietf.org/html/draft-ietf-oauth-json-web-token-27 • JSON Web Signature (JWS) http://tools.ietf.org/html/draft-ietf-jose-json-web-signature-33 • JSON Web Encryption (JWE) http://tools.ietf.org/html/draft-ietf-jose-json-web-encryption-32