Hardening WordPress: Practical Security Lessons from Real Incidents
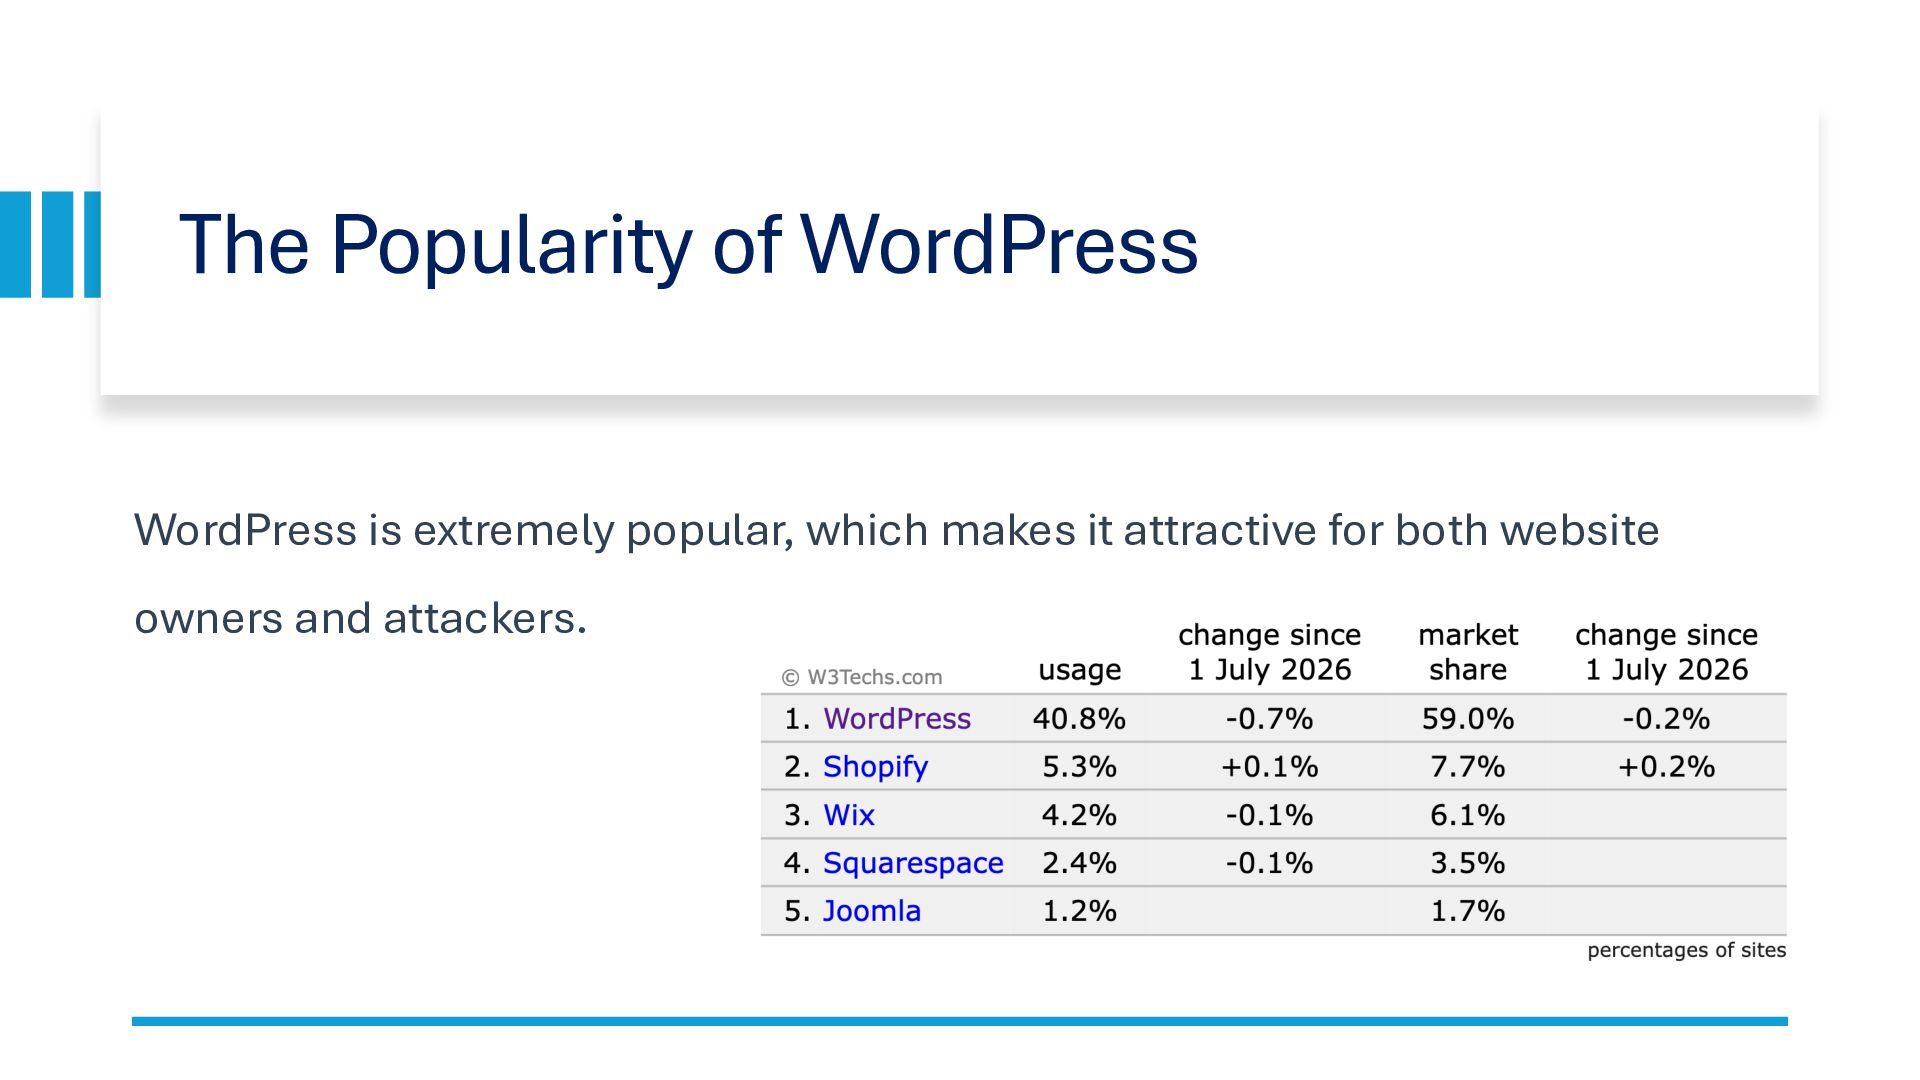
WordPress powers a significant portion of the web, making it an attractive target for cybercriminals. While security plugins and web application firewalls provide important protection, real-world experience demonstrates that securing a WordPress website requires a much broader approach.
This presentation, delivered by Haim Michael at The H@ck Summit 2026 in Poland, explores practical WordPress security lessons learned from real incidents involving compromised websites. Rather than focusing exclusively on theoretical vulnerabilities, the presentation examines concrete measures that can reduce the attack surface, strengthen website defenses, and improve recovery from security incidents.
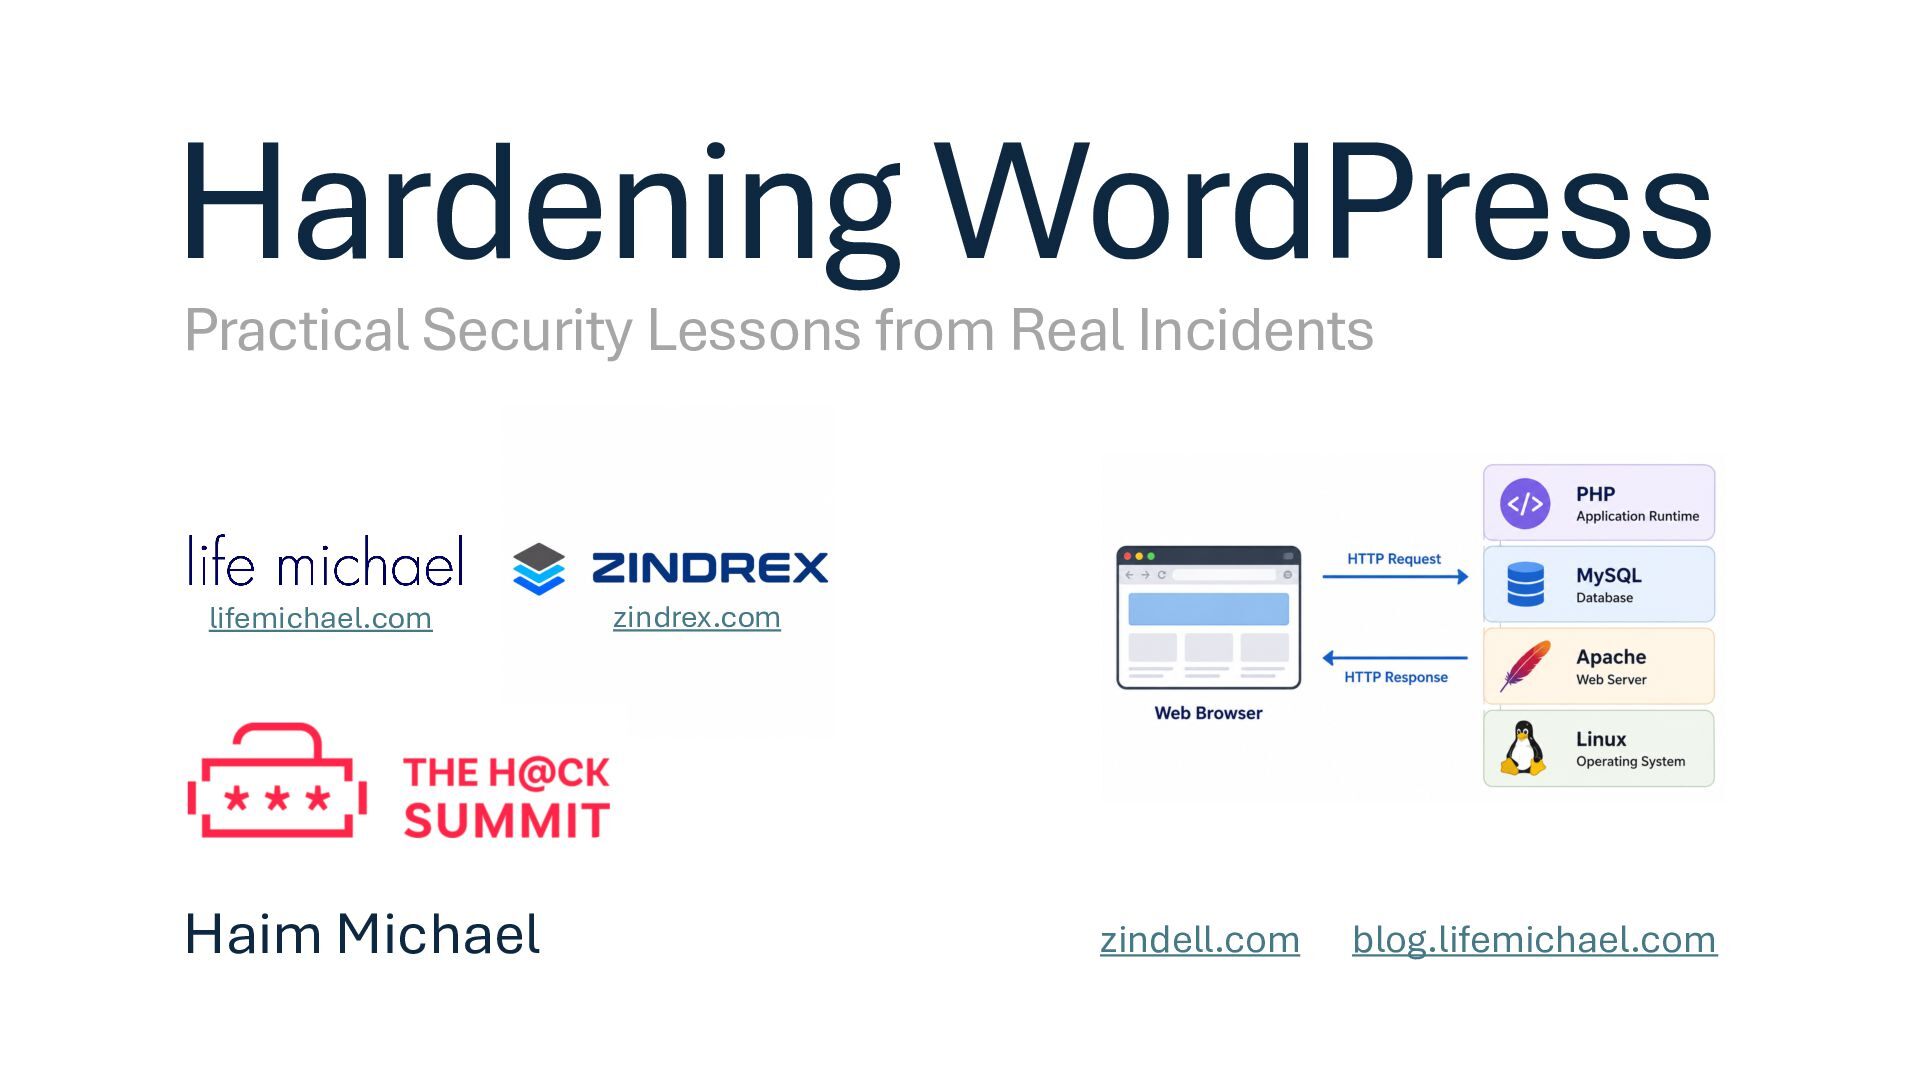
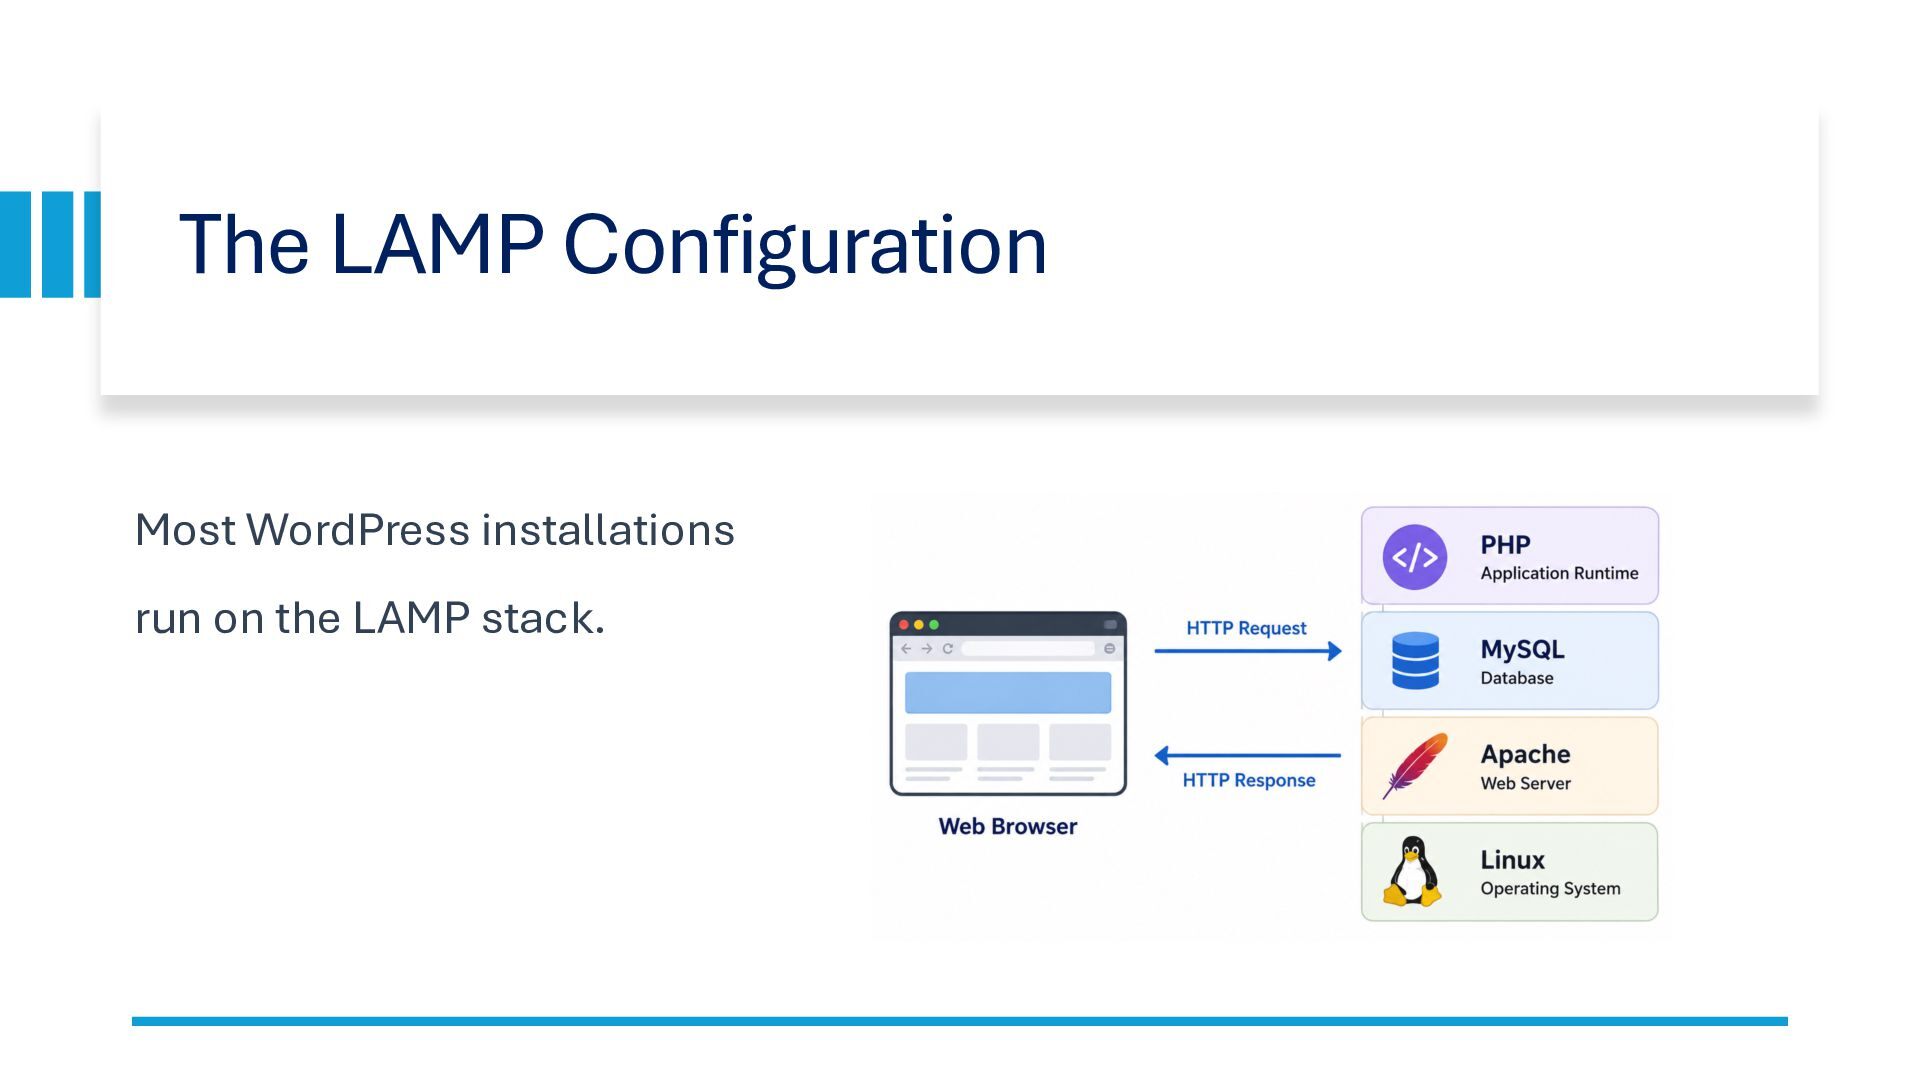
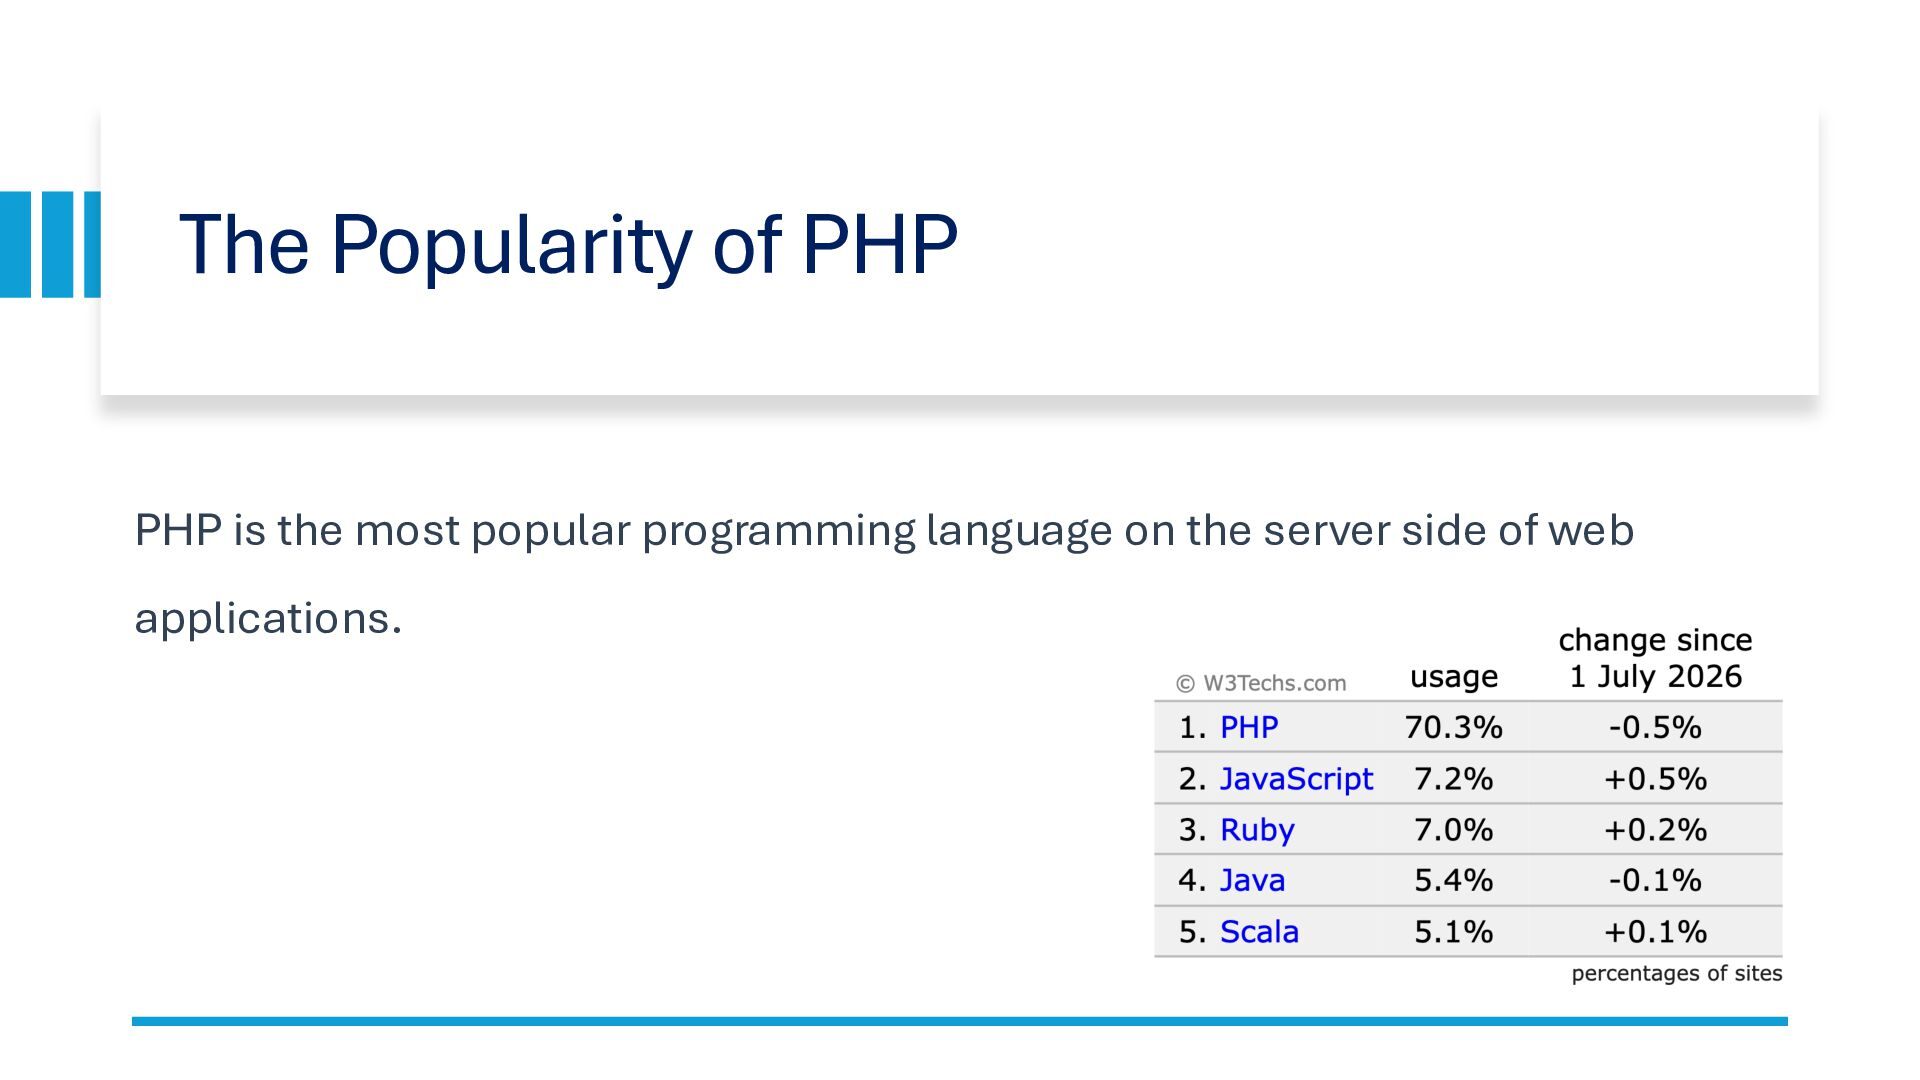
The presentation begins with an overview of WordPress, its underlying LAMP architecture, and the implications of its widespread adoption. It then introduces practical security recommendations based on experience managing and securing WordPress websites.
Topics covered in the slides include:
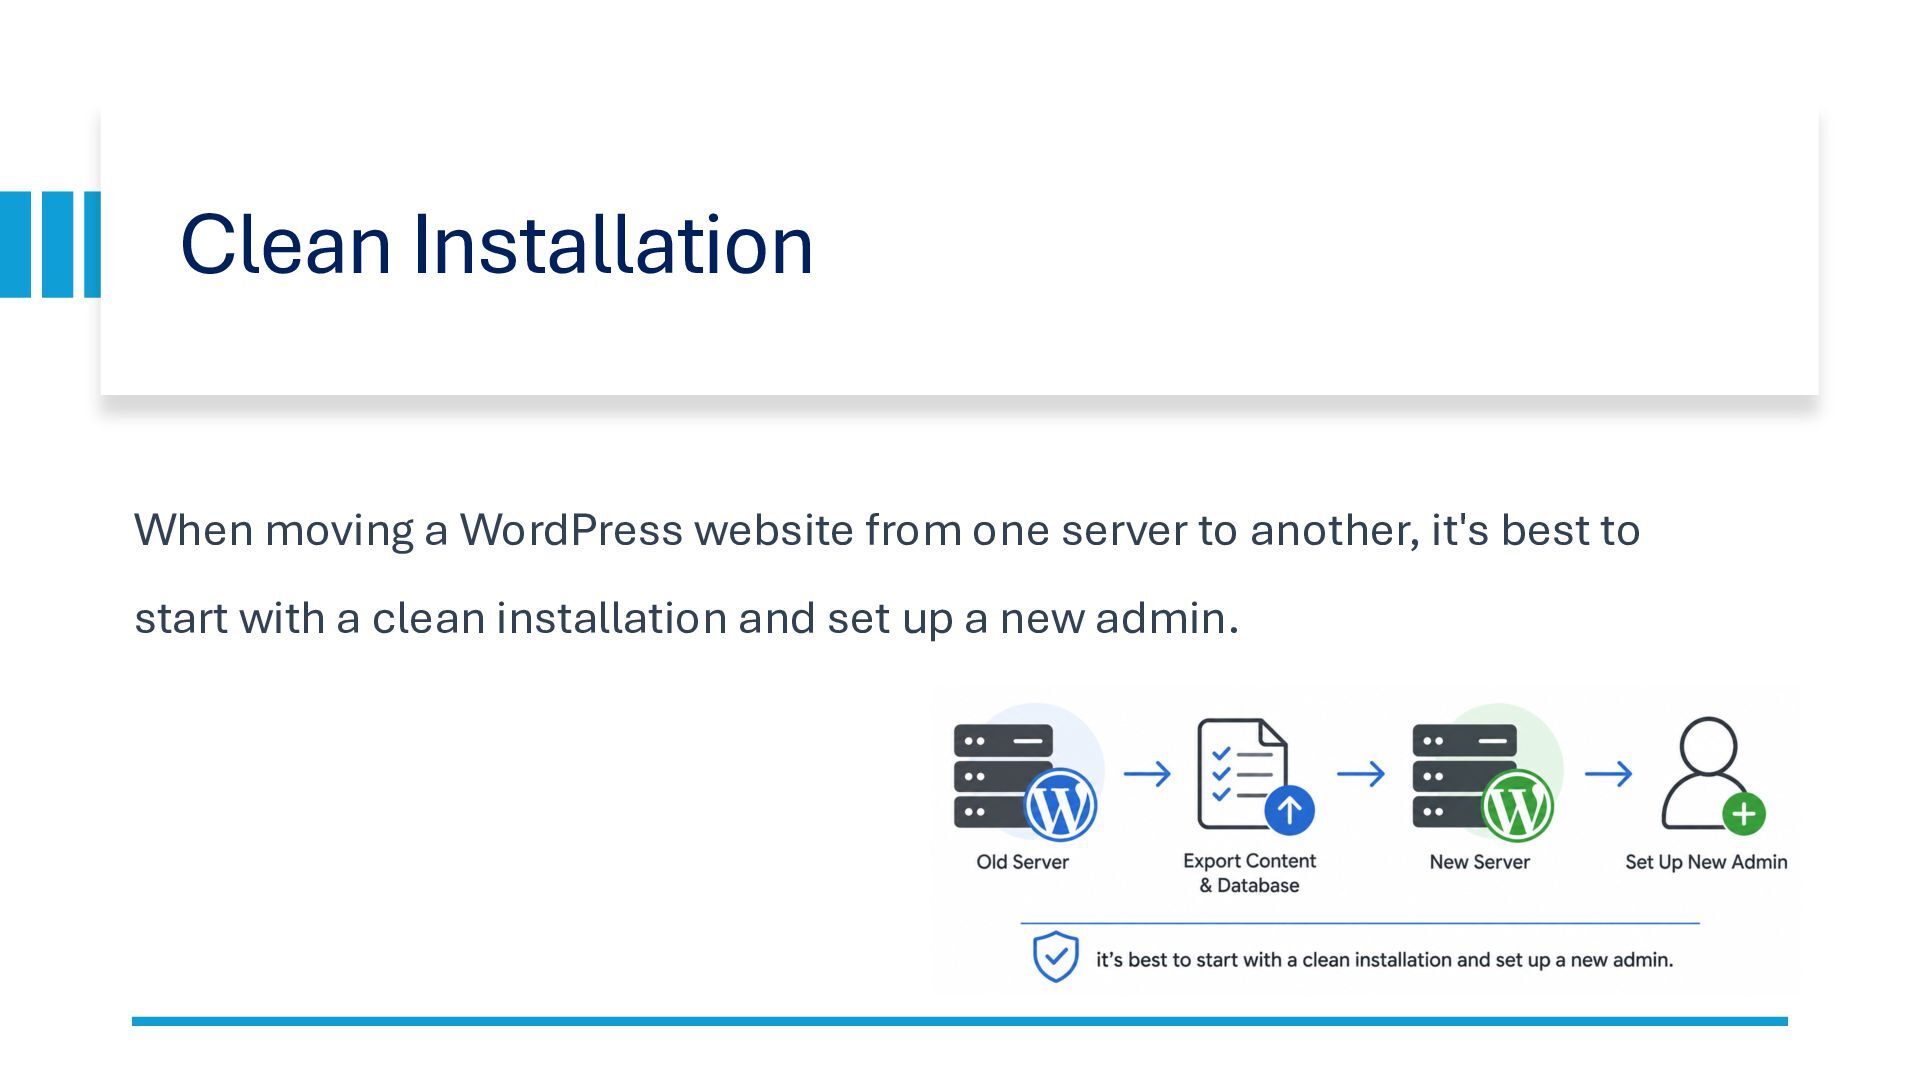
Clean Installations and Secure Recovery: Rebuilding or migrating compromised WordPress installations without carrying over potentially malicious files or backdoors.
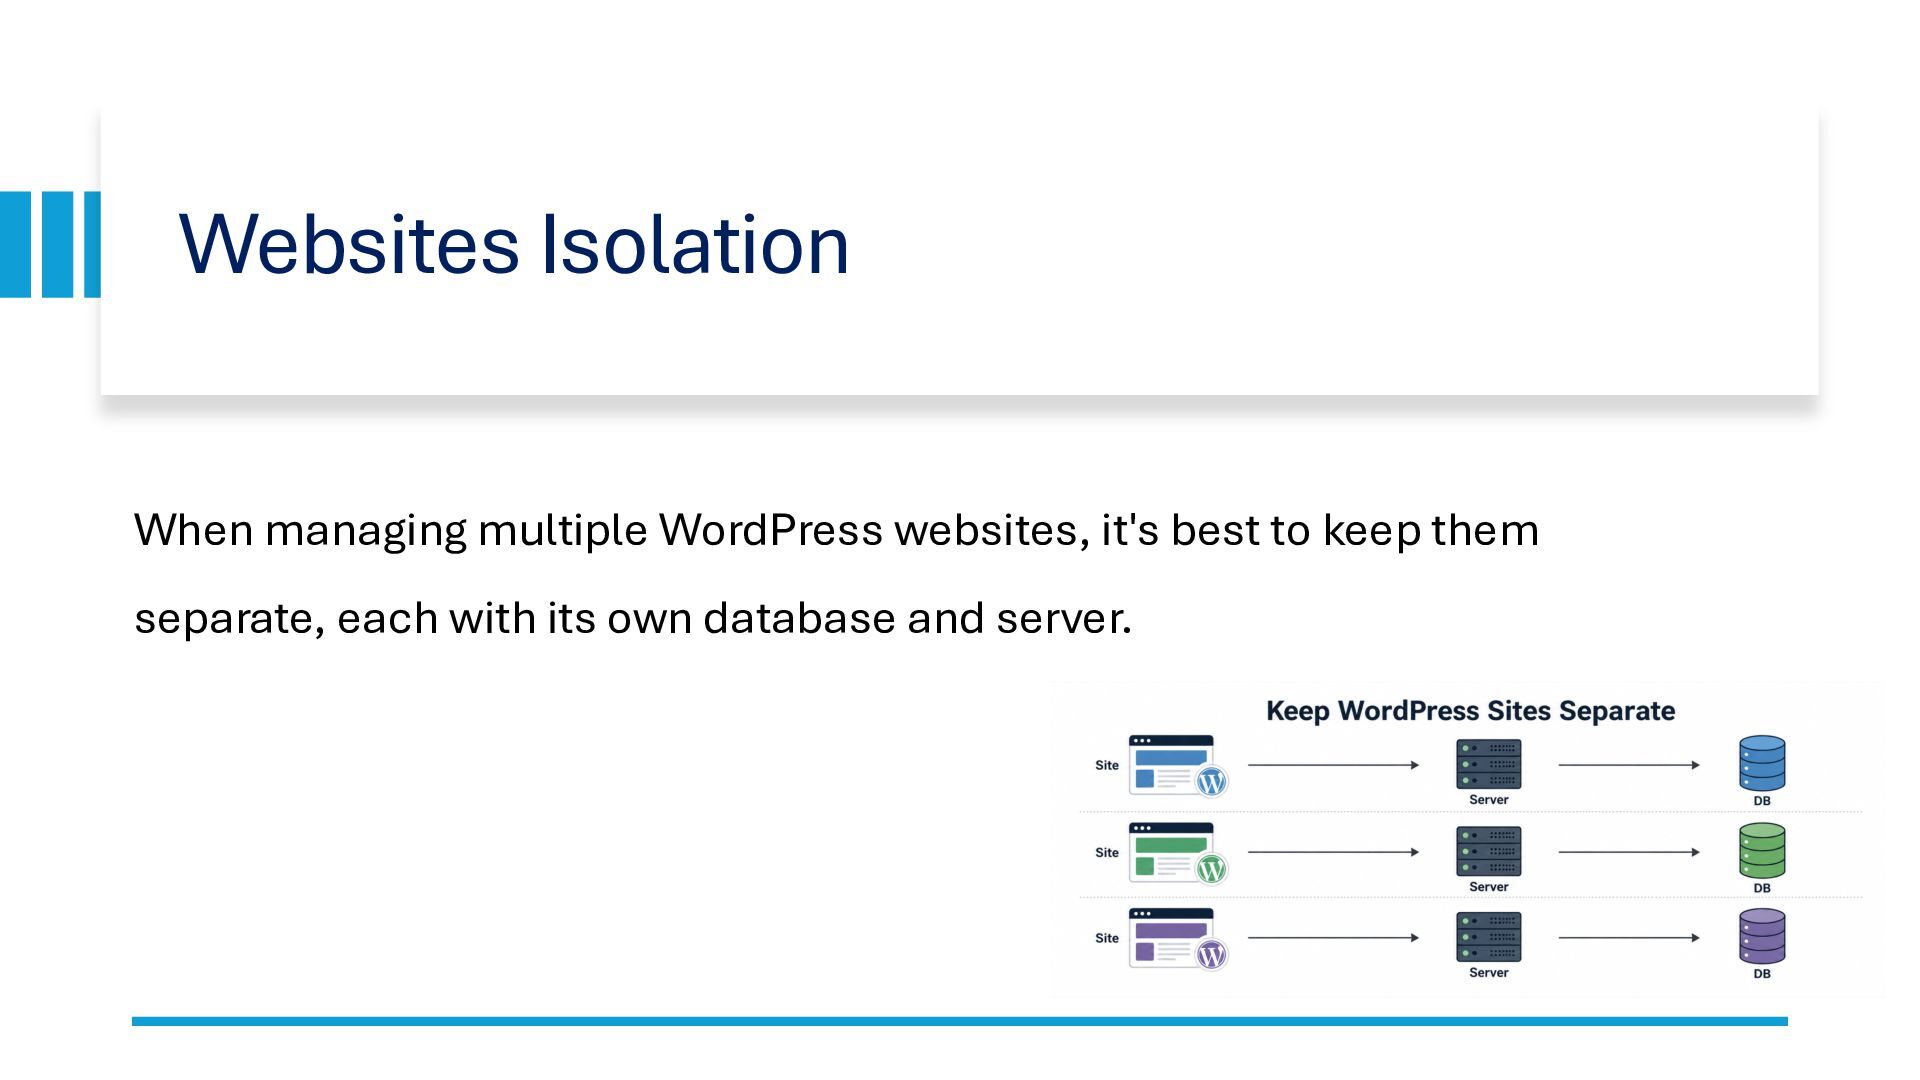
Website Isolation: Separating WordPress installations, databases, and hosting environments to limit the impact of security incidents.
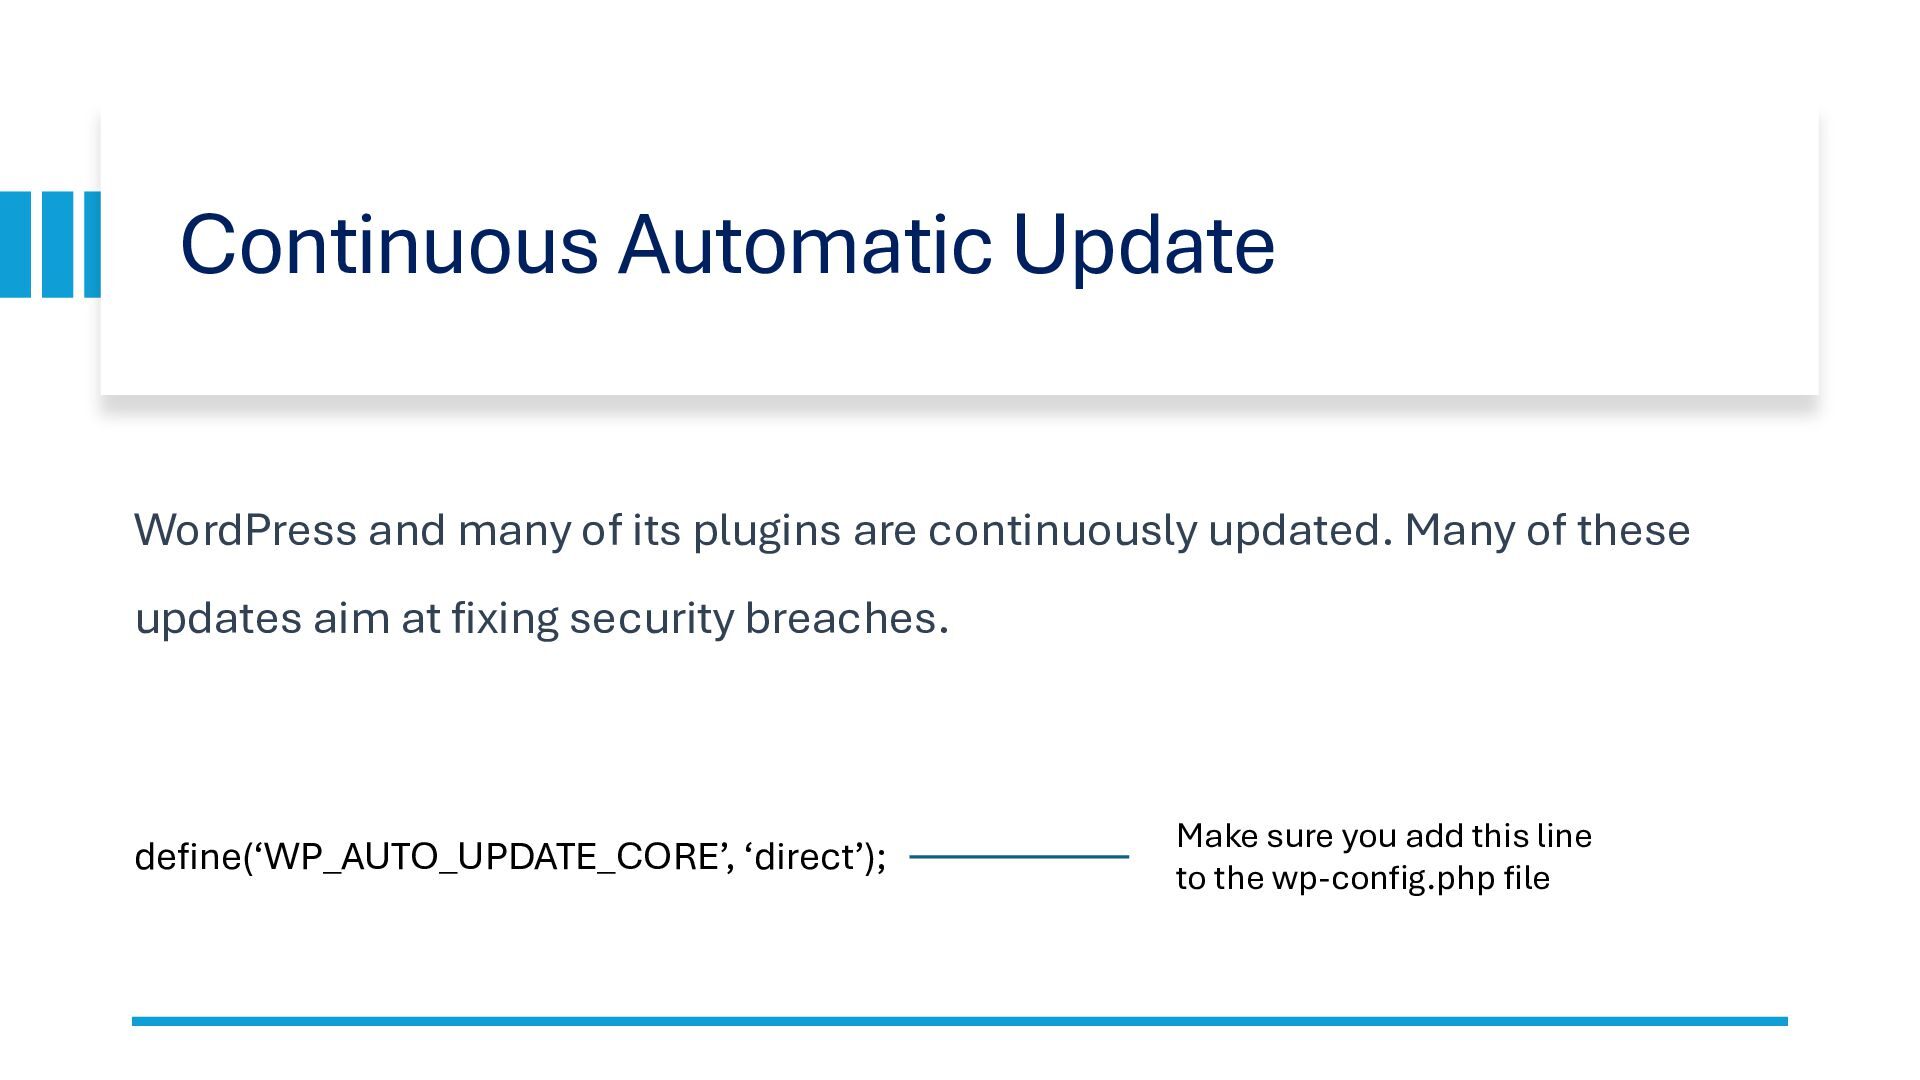
Updates and Maintenance: Keeping WordPress core, plugins, and themes updated while reducing unnecessary components.
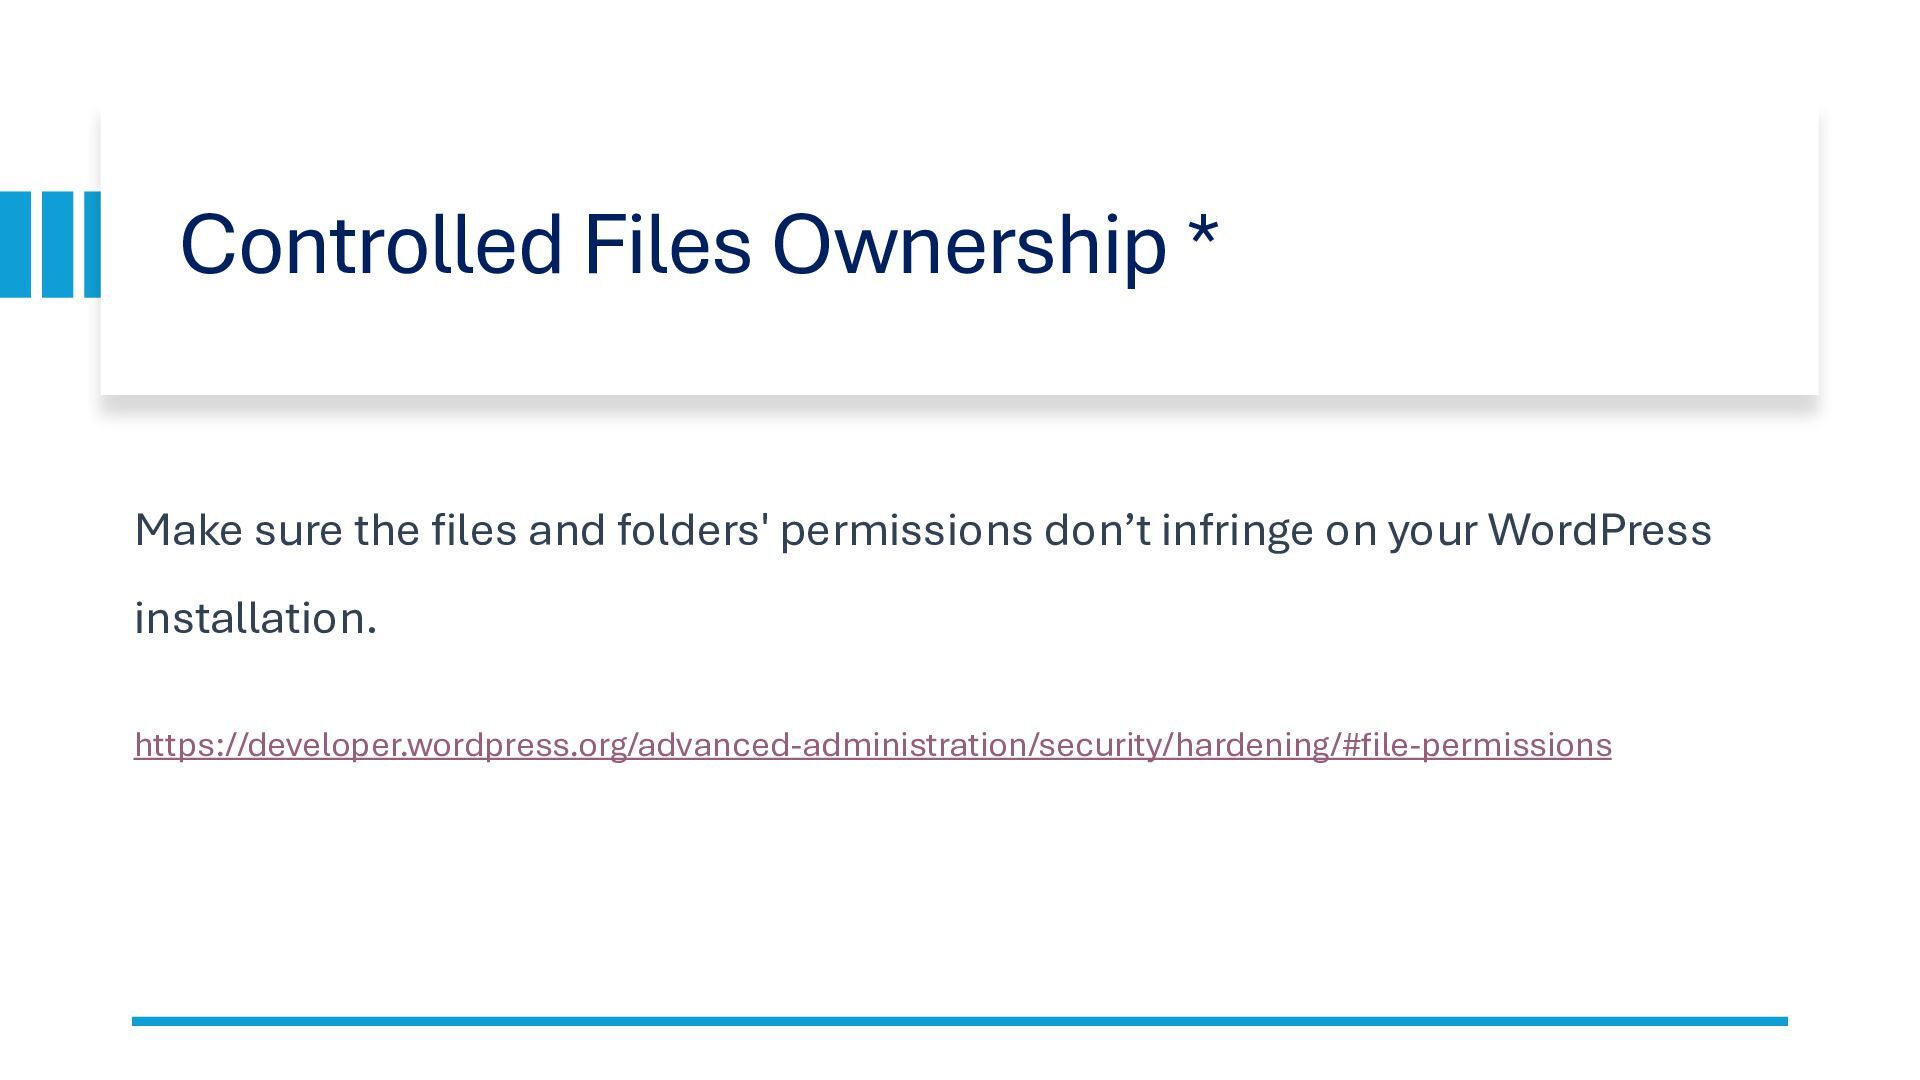
File Permissions and Ownership: Protecting the WordPress file system through appropriate access controls and secure ownership configurations.
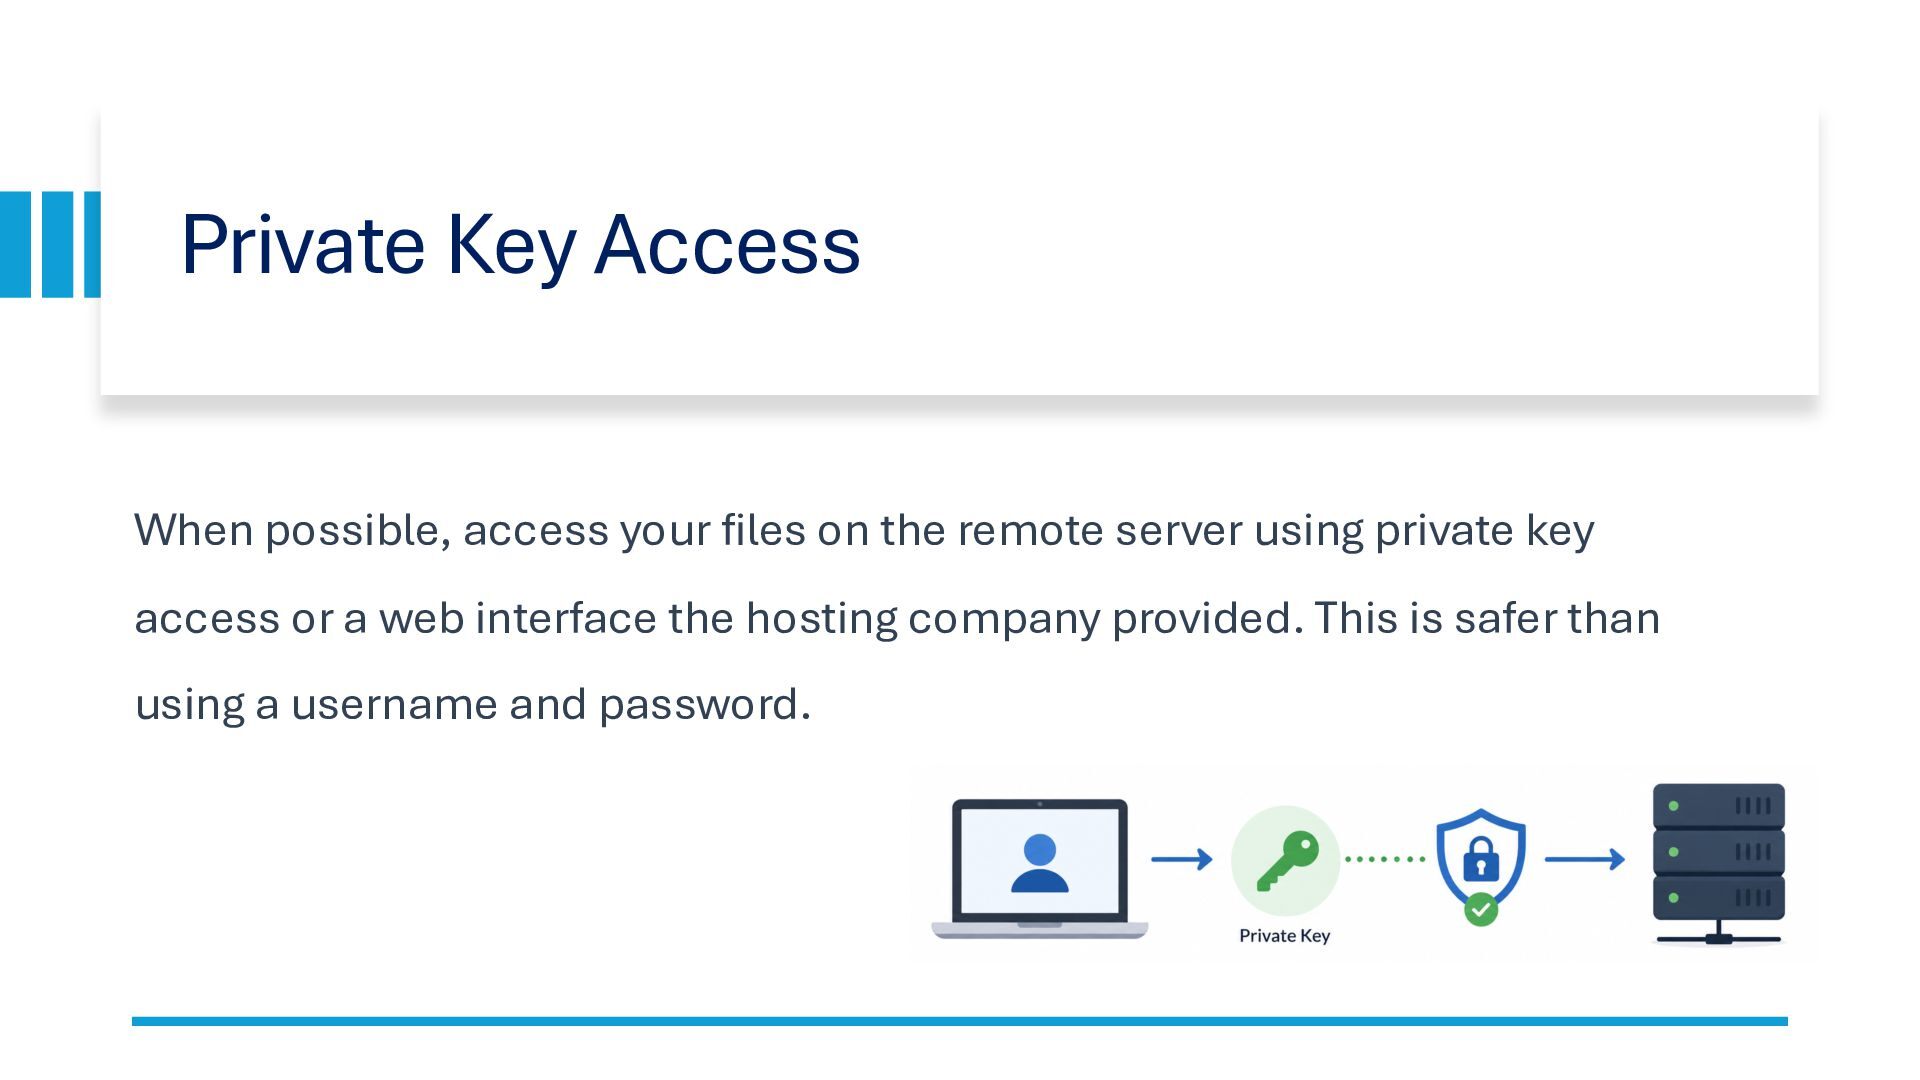
Authentication and Access Control: Strengthening administrator access through two-factor authentication, private-key access, and additional login protections.
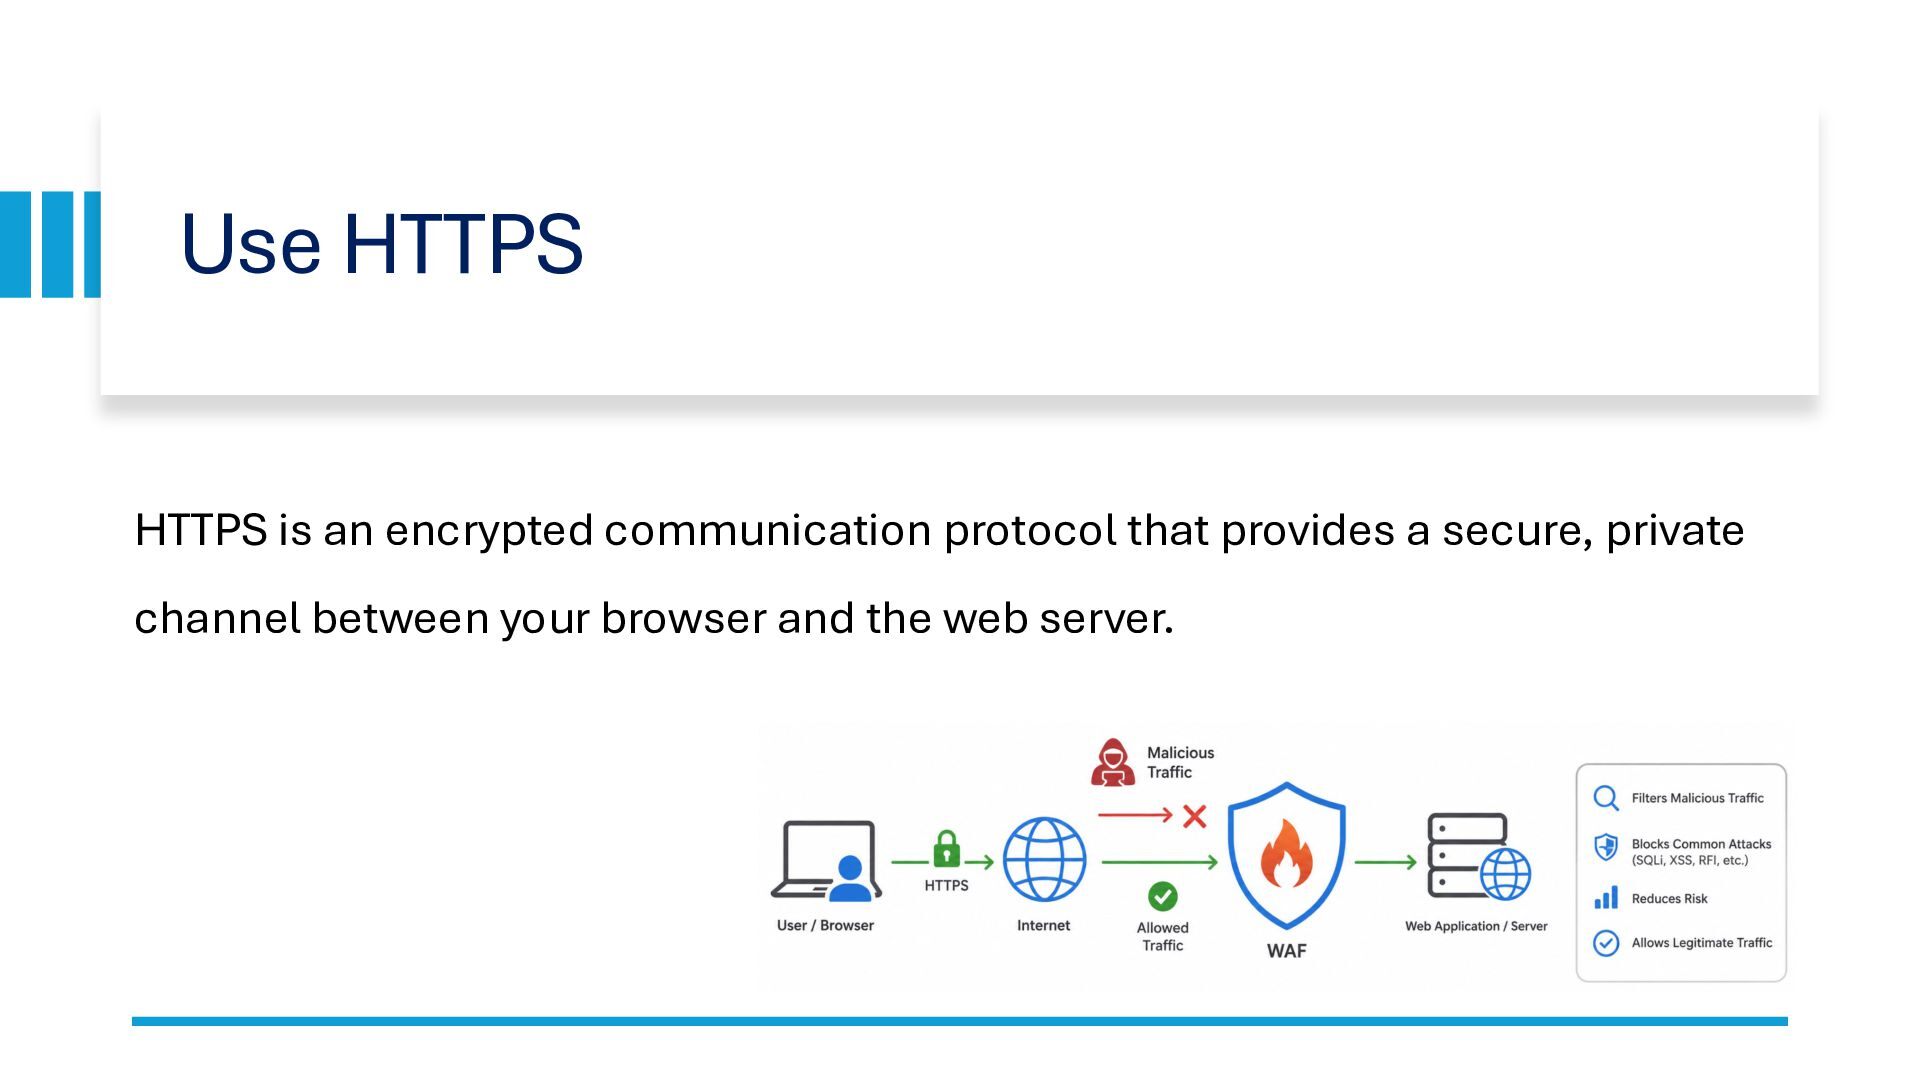
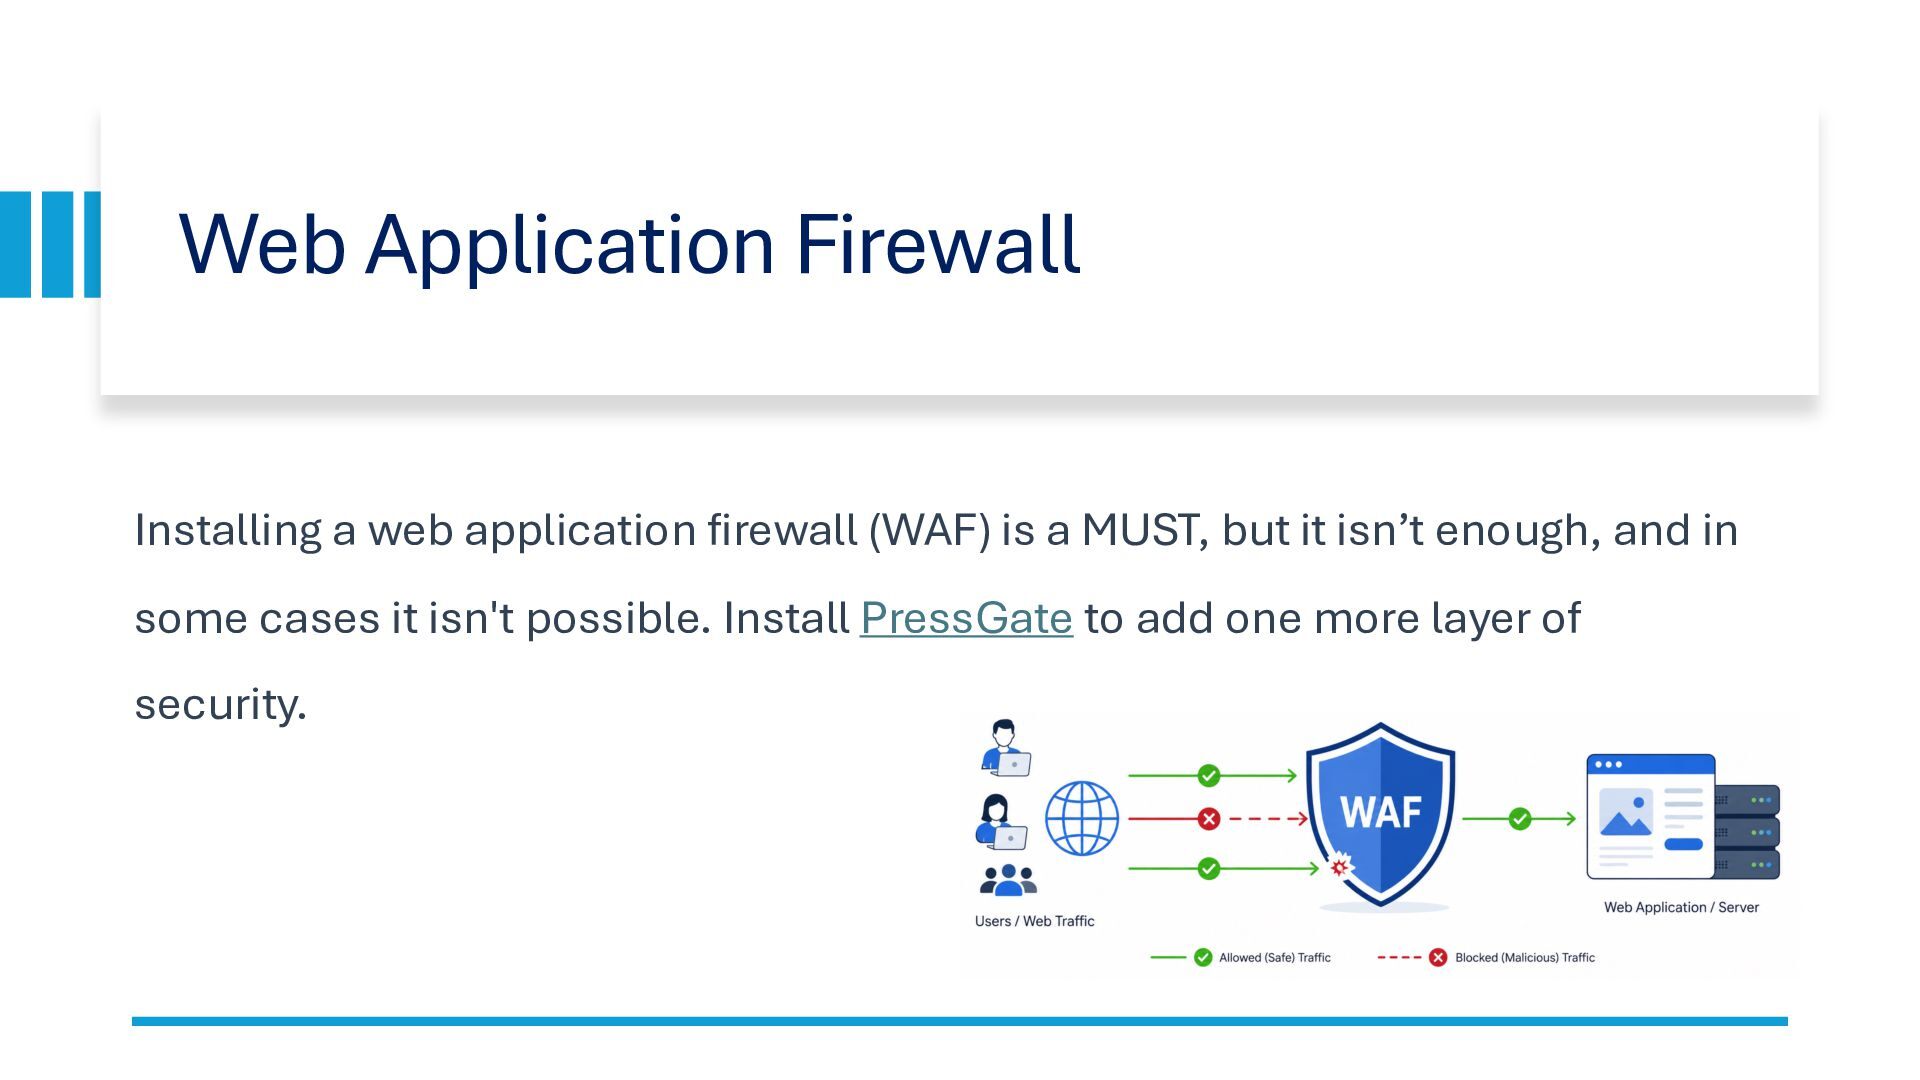
Web Application Firewalls: Understanding the benefits and limitations of WAFs and introducing PressGate as an additional layer of WordPress security.
Reducing the Attack Surface: Minimizing exposed services, administrative tools such as phpMyAdmin, unnecessary plugins, and unused themes.
Operational Security: Treating security as a continuous responsibility rather than a one-time configuration task.
Beyond WordPress: Considering static websites as an alternative architecture that can eliminate entire categories of WordPress-related security risks.
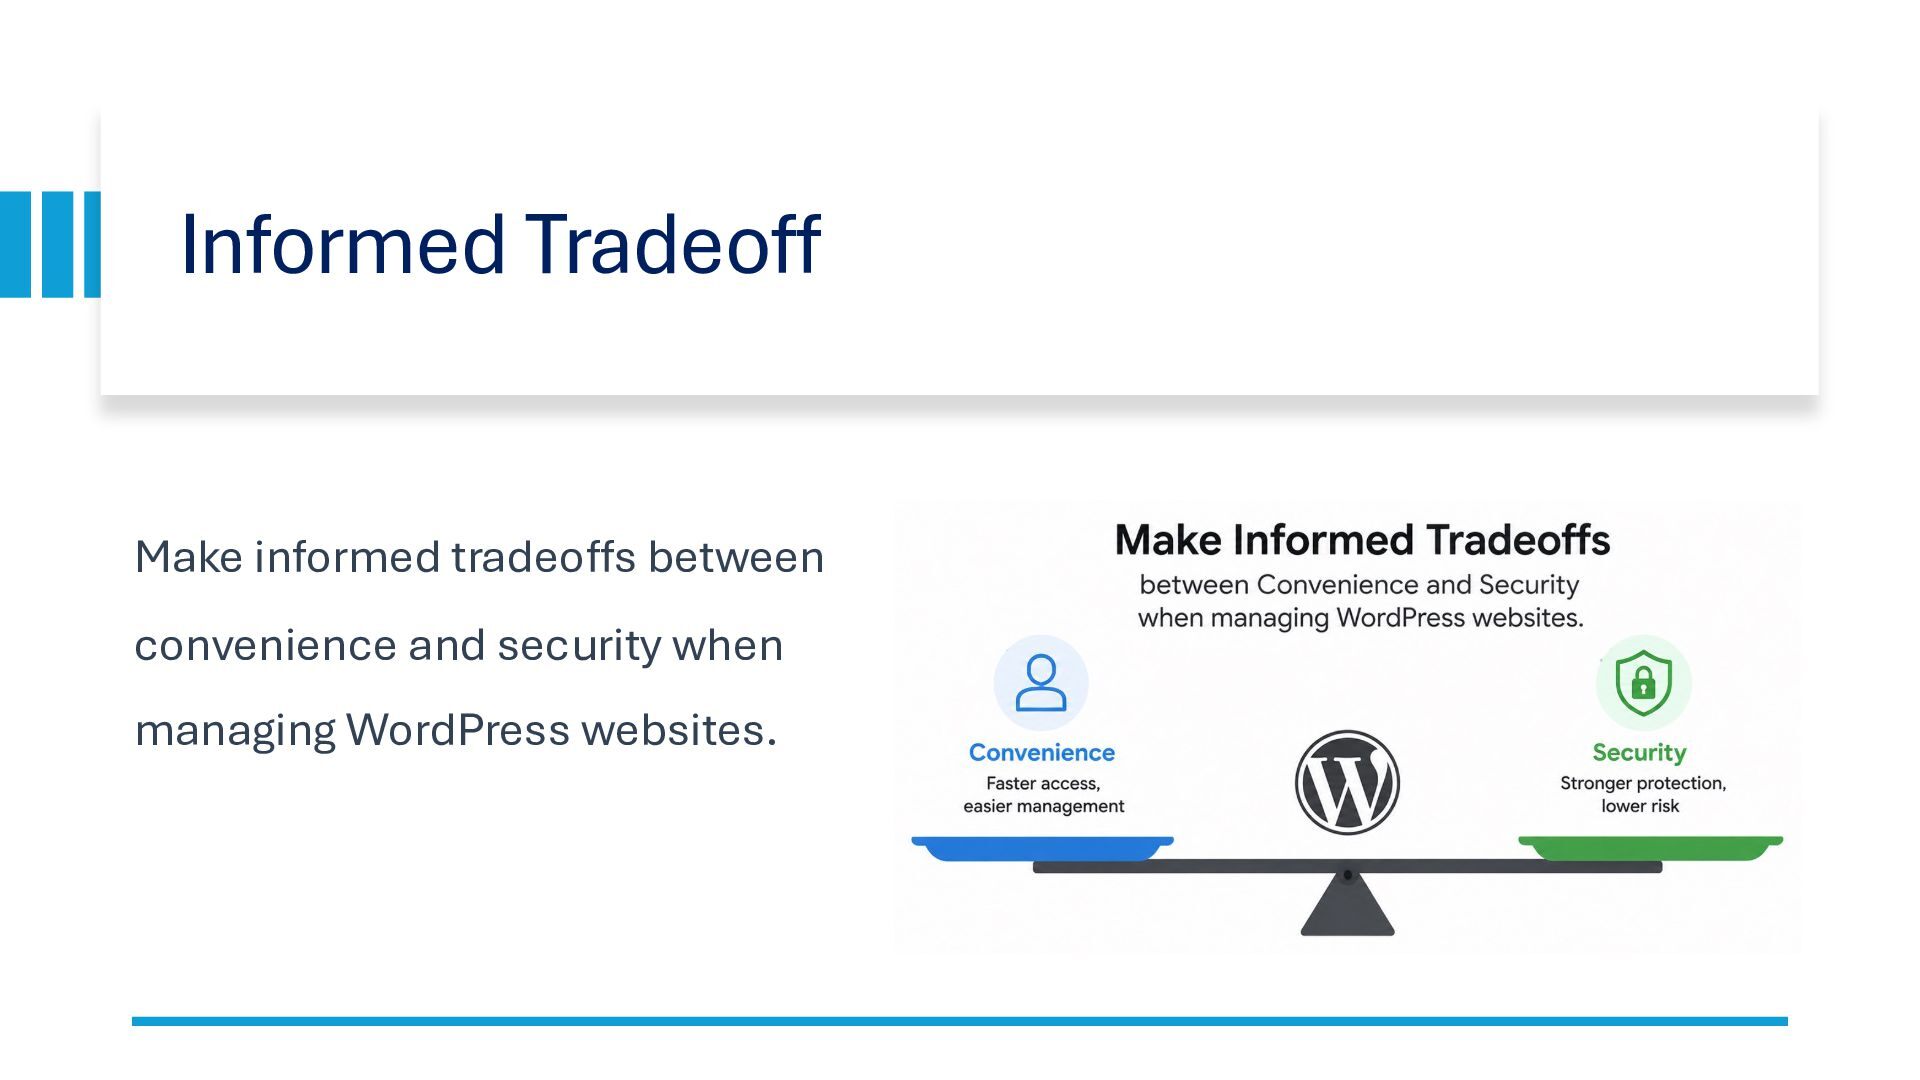
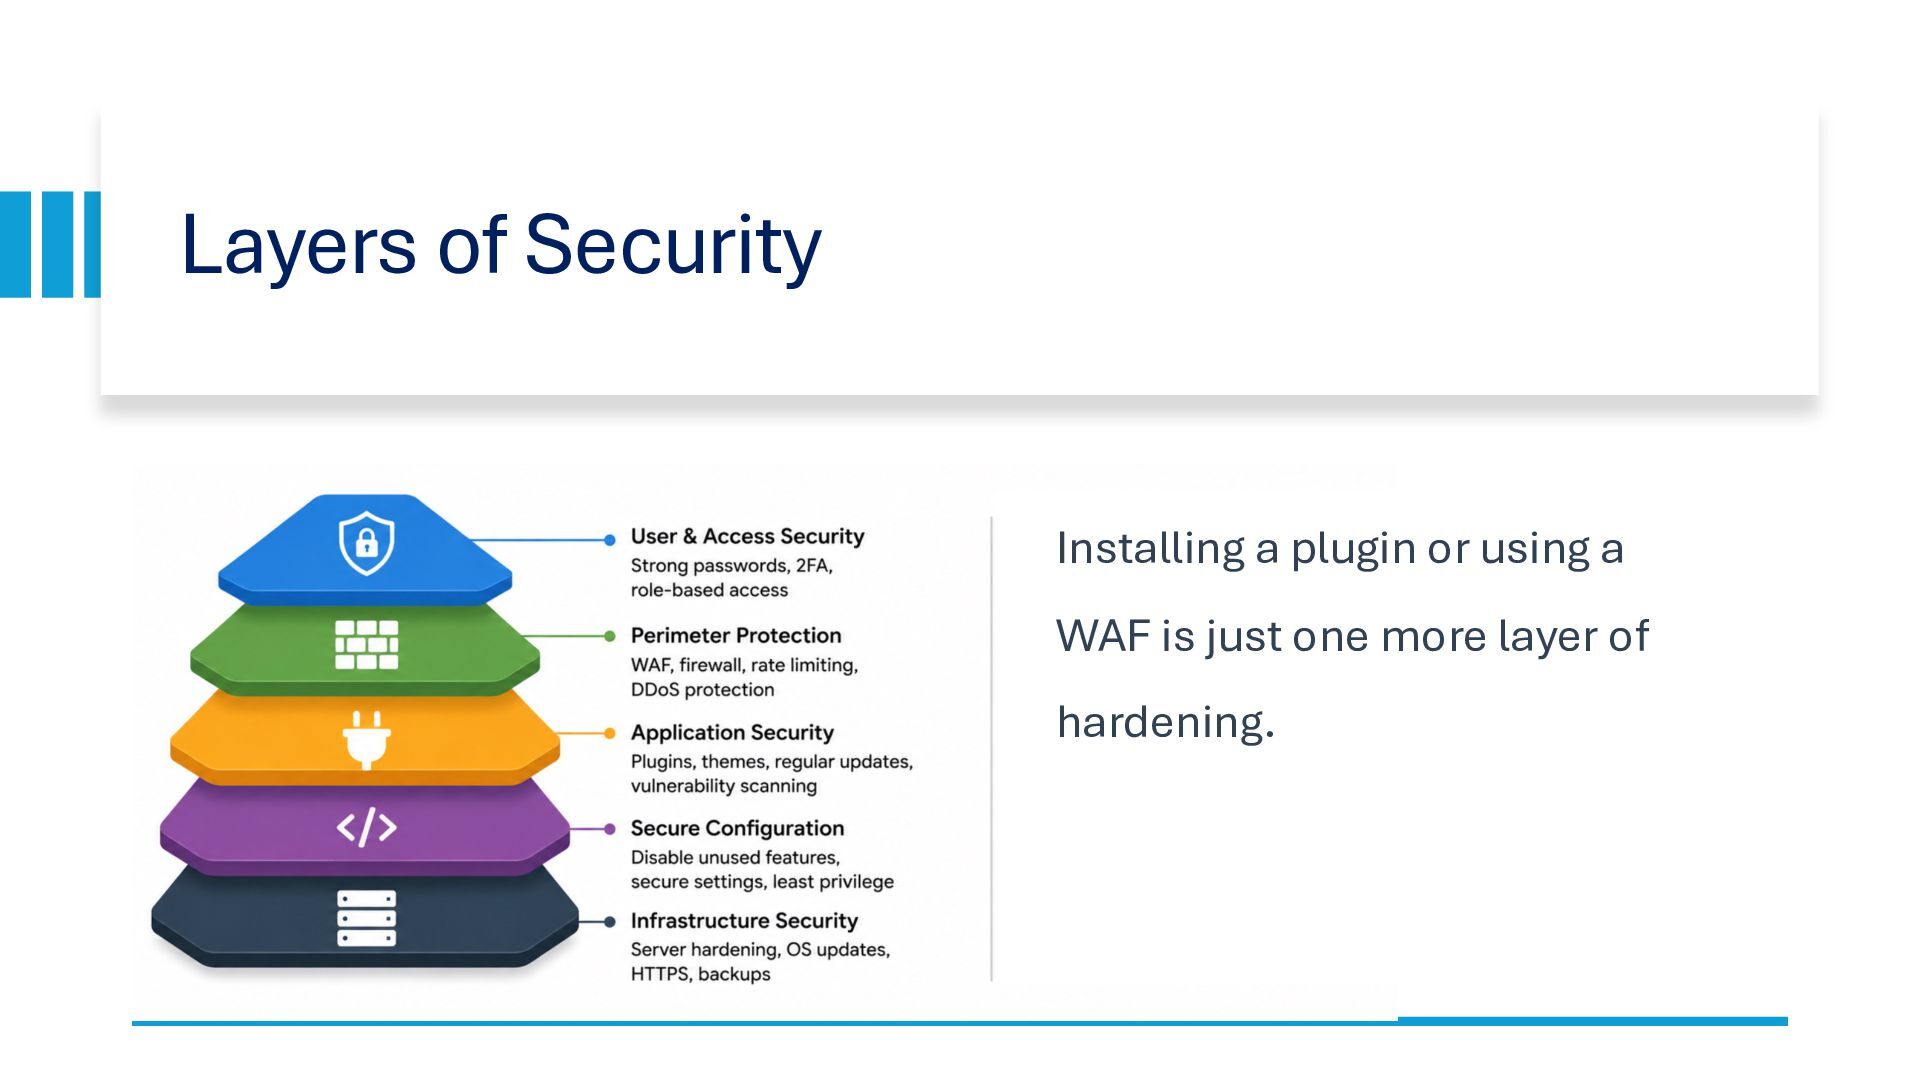
A central message of this presentation is that WordPress security is not achieved by installing a single plugin or enabling a firewall. Effective protection requires a layered approach combining secure configuration, access control, regular maintenance, isolation, monitoring, and informed architectural decisions.
The lessons extend beyond WordPress. Many of the principles discussed are equally relevant to securing web applications built with other technologies.
These slides are intended for WordPress developers, website administrators, software engineers, DevOps professionals, cybersecurity practitioners, and anyone responsible for maintaining secure web applications.
Conference: The H@ck Summit 2026
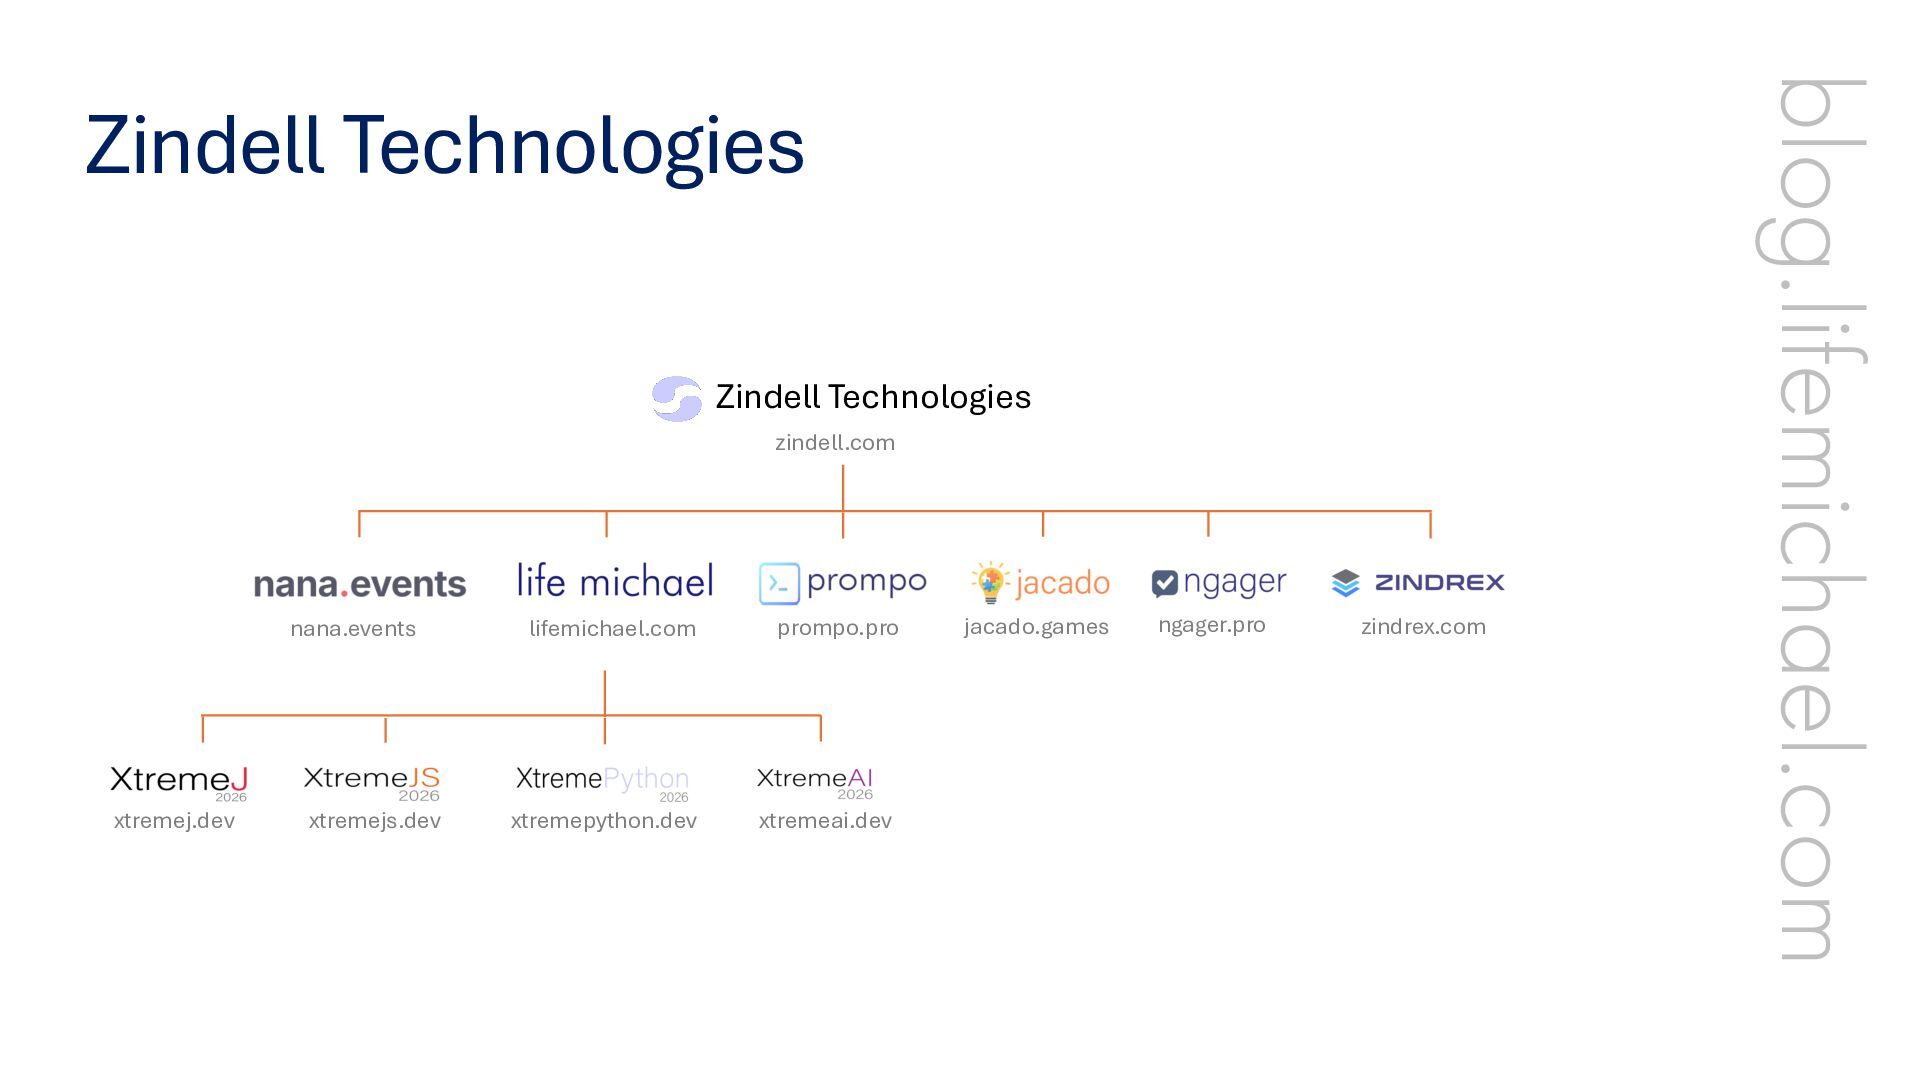
Speaker: Haim Michael, Founder & CEO, Zindell Technologies
Conference website: https://thehacksummit.com/en/
WordPress security with PressGate: https://zindrex.com/pressgate
Speaker's website: https://lifemichael.com
Zindrex Website: https://zindrex.com
The Video on YouTube: https://youtu.be/y9BWZt4wa98

 lifemichael
 akihiro0038
 bengo4com
 a_suenami
 daitak
 tomoki10
 carta_engineering
 kazatohiei
 ymotongpoo
 atalie2m
 biwashi
 hagino3000
 amarelo_n24
 apolaine
 techseoconnect
 sergeychernyshev
 ipullrank
 aleyda
 rakko
 reverentgeek
 akademiya2063
 mkilby
 lcolladotor
 eileencodes
 mlcsv