Surviving WAF Bypass: Building Stronger Authent...
 SiteGround - Reliable hosting with speed, security, and support you can count on.

Surviving WAF Bypass: Building Stronger Authentication Defenses for WordPress Websites
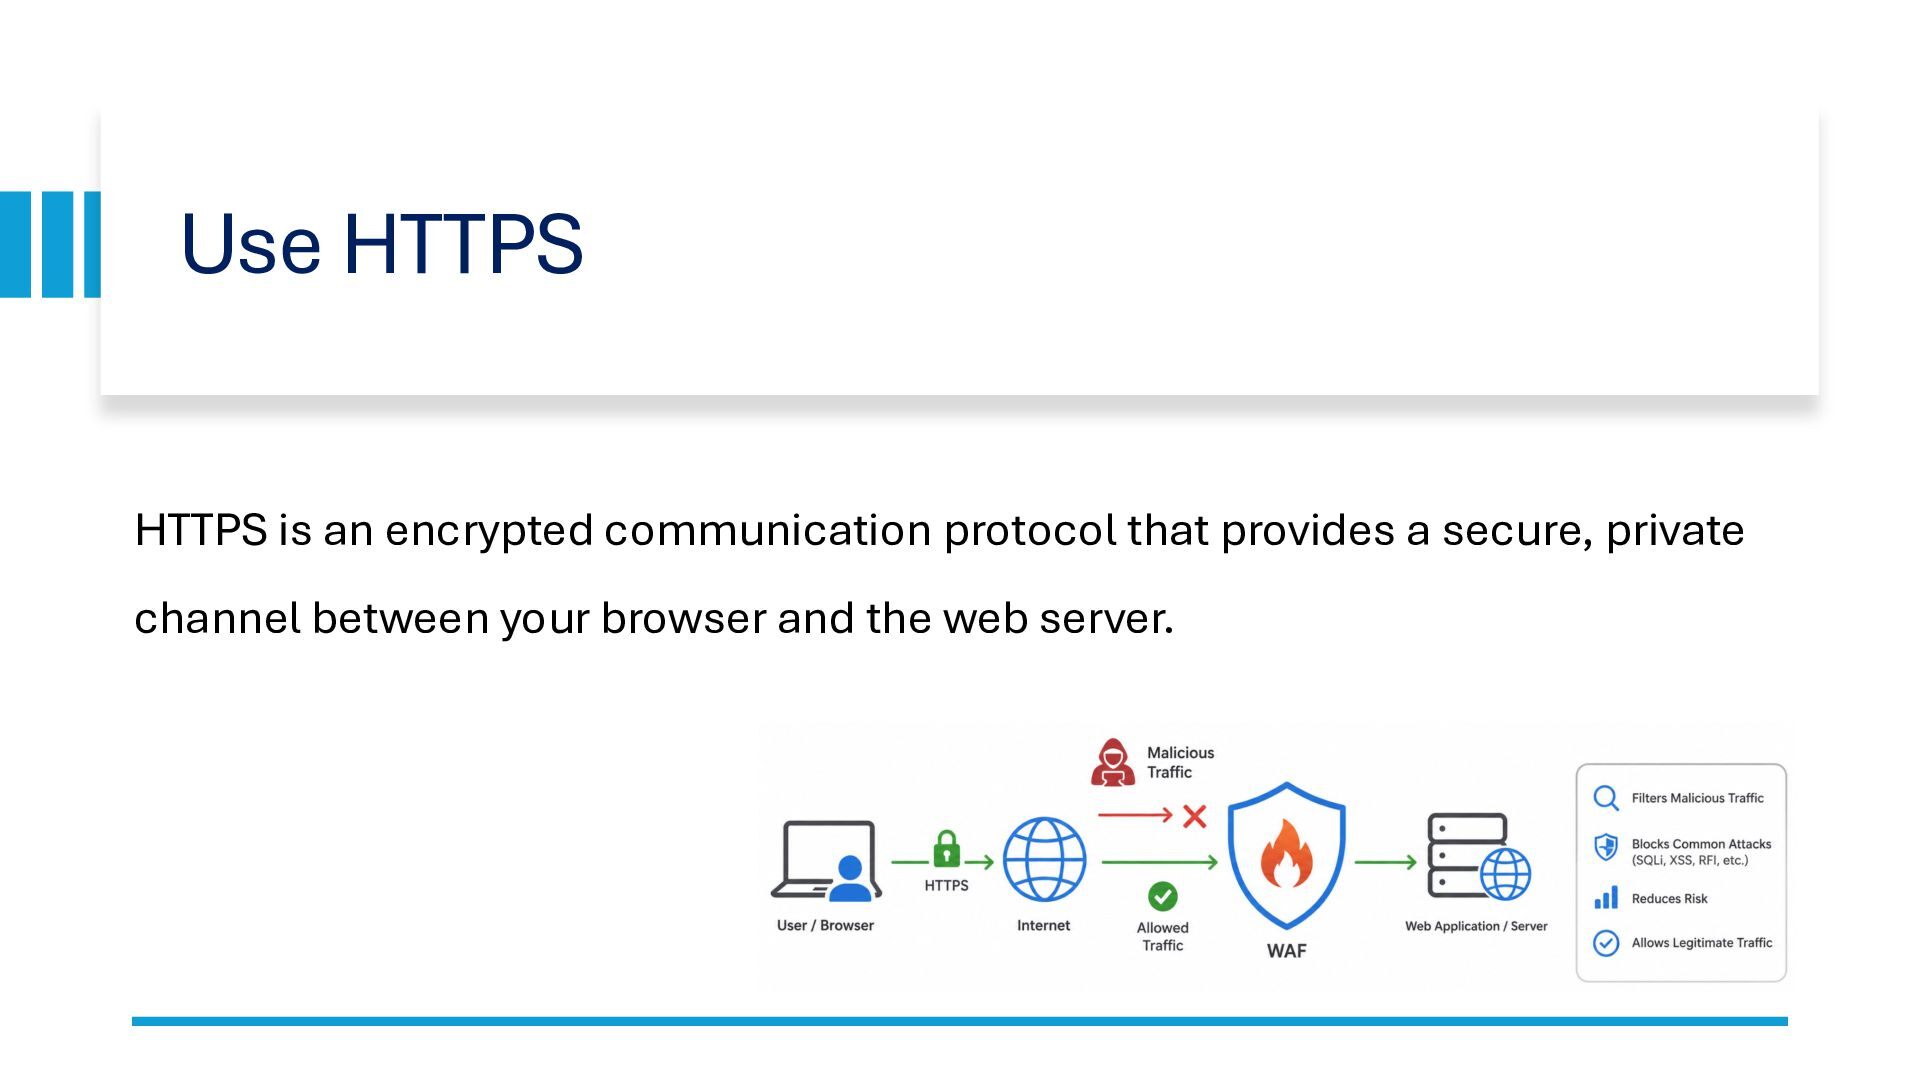
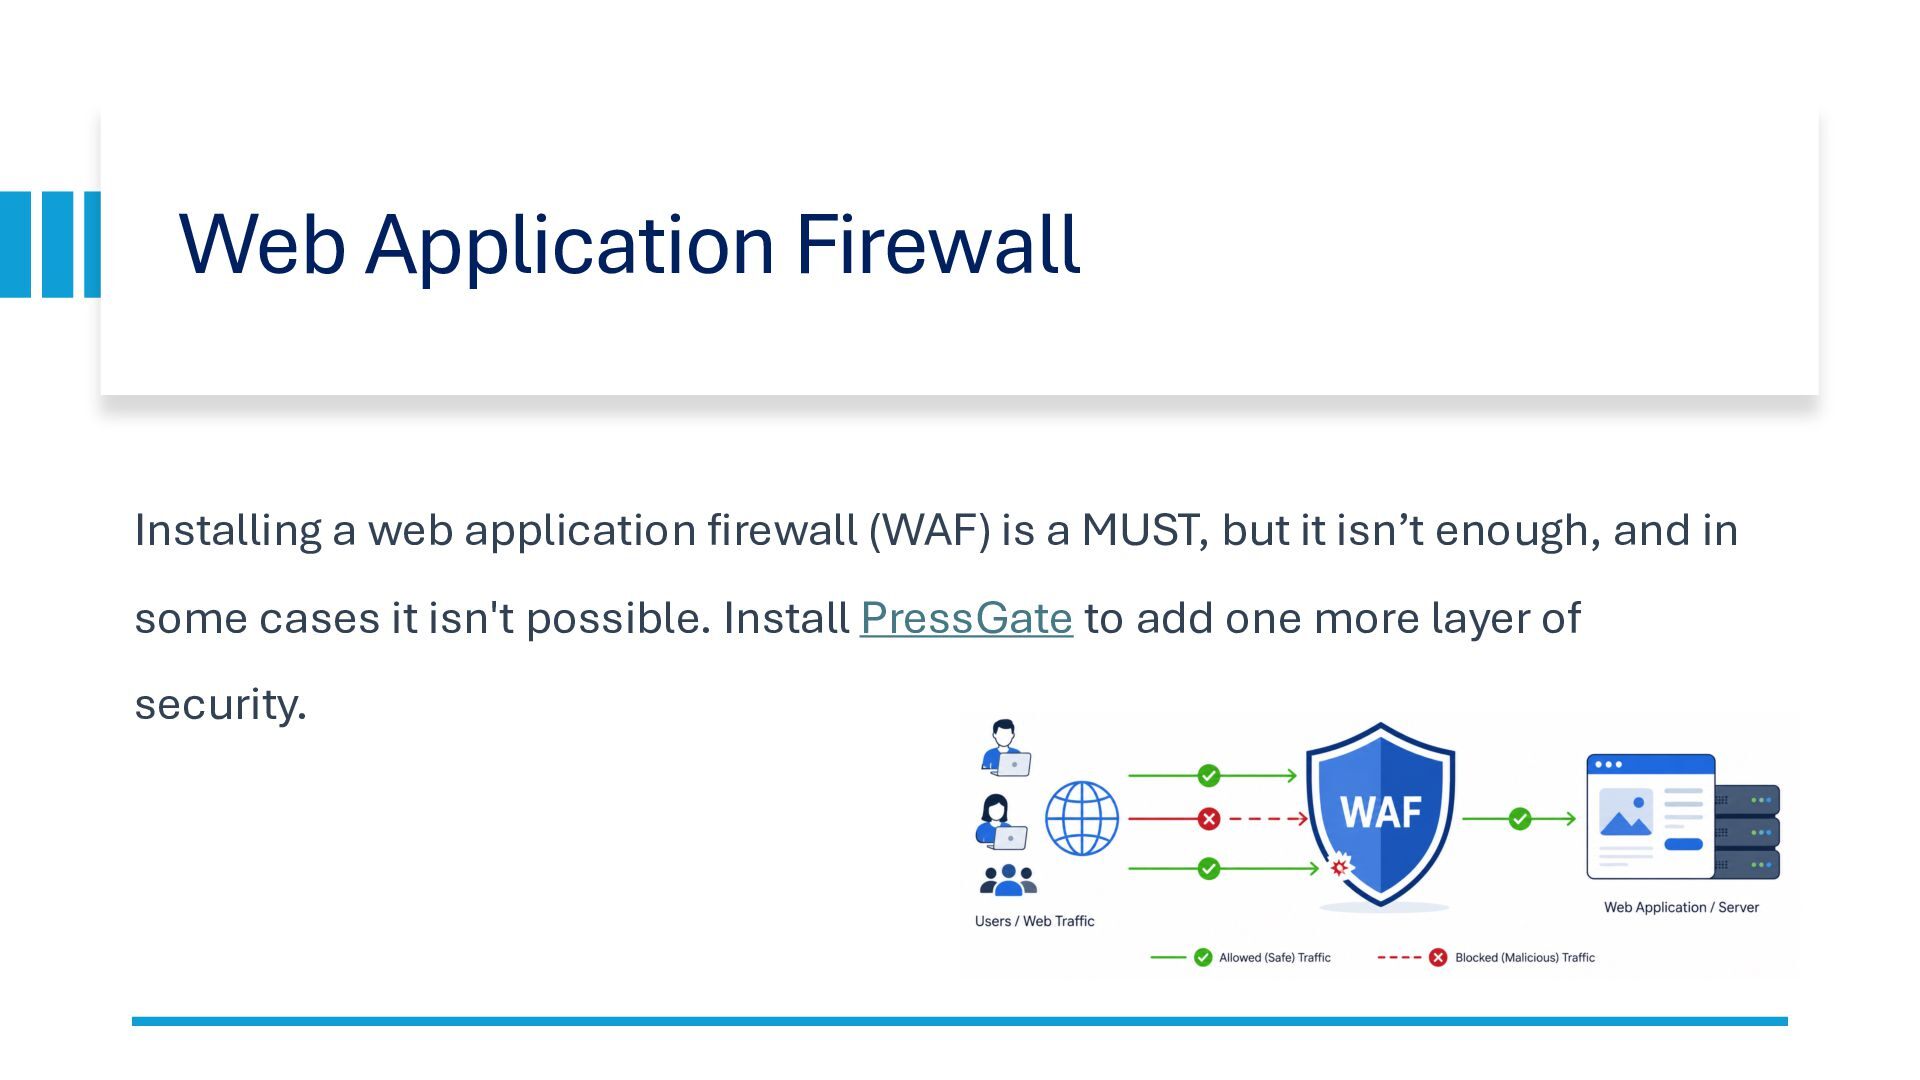
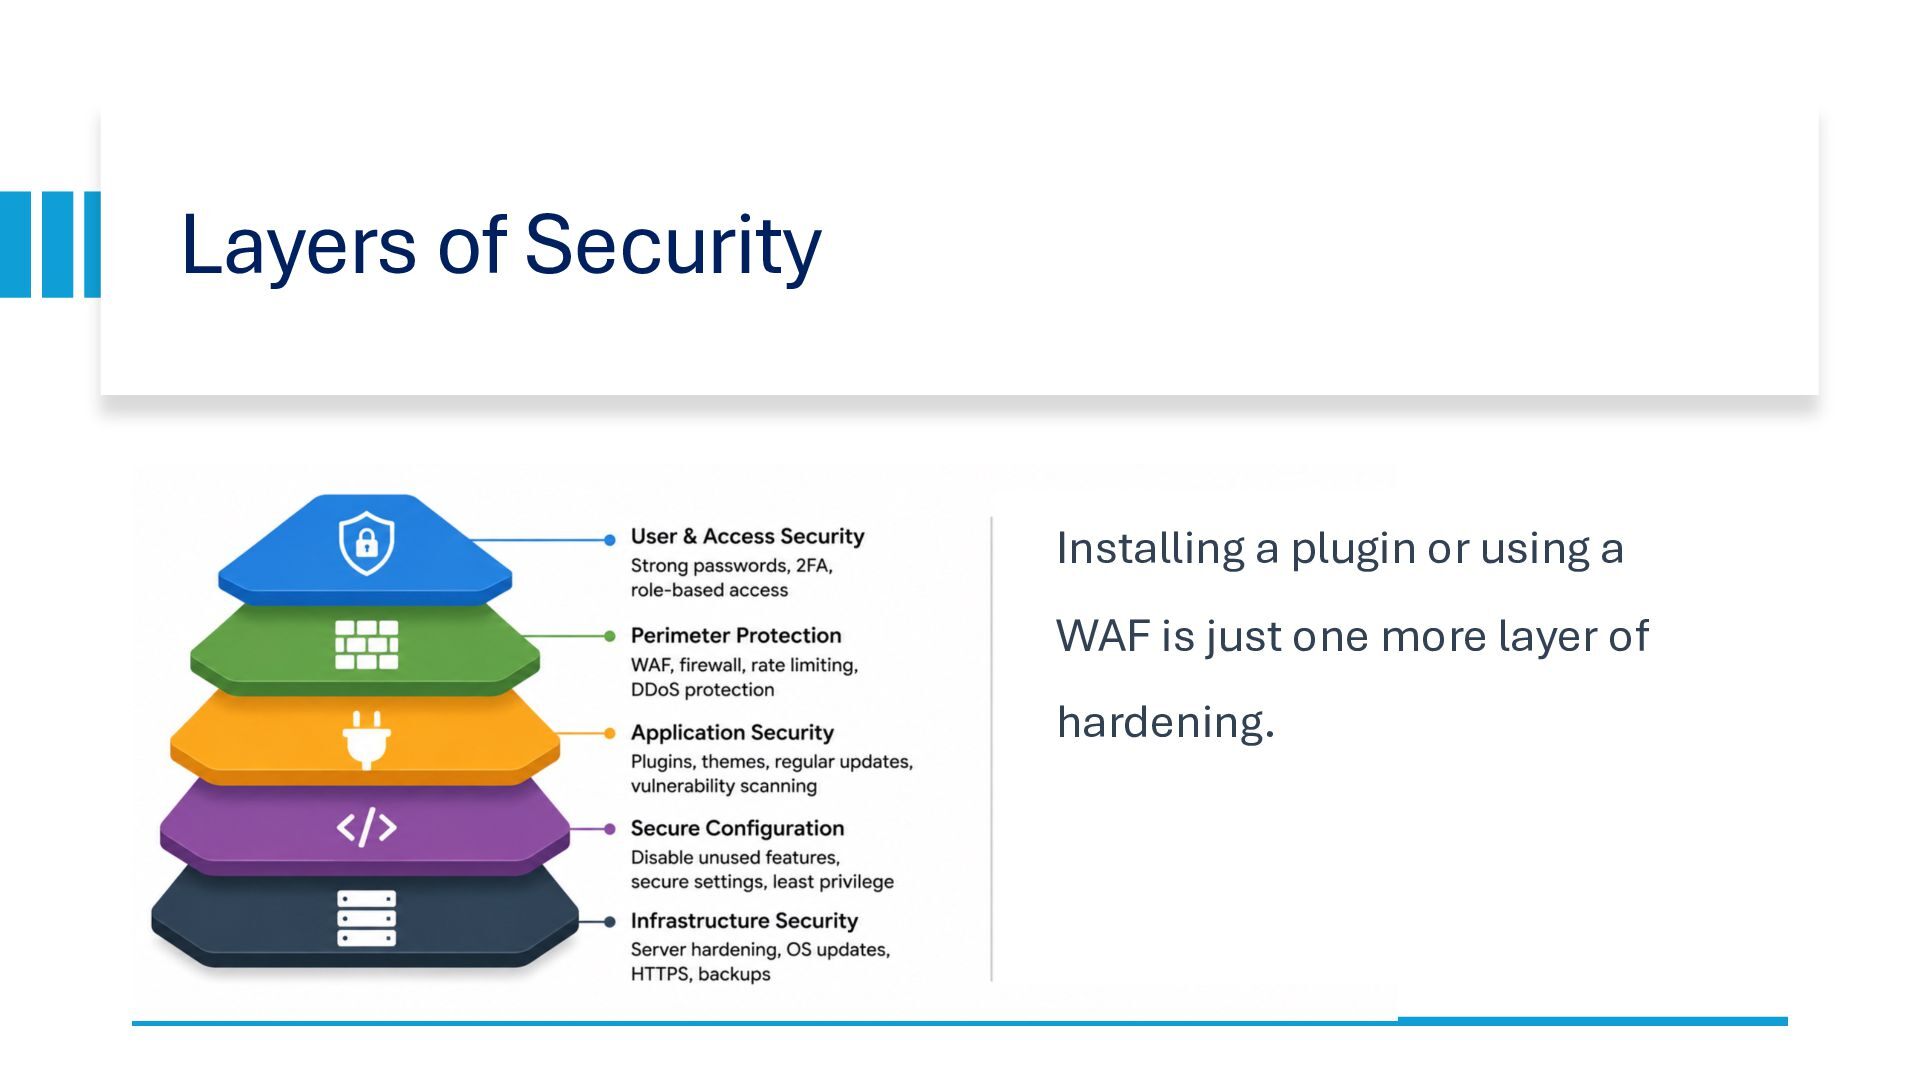
Securing a WordPress website requires much more than installing a security plugin or configuring a Web Application Firewall (WAF). Even with a WAF in place, attackers can bypass security controls and exploit weaknesses in authentication, server configuration, and website administration.
These slides, presented at WordCamp Sofia 2026 on October 24, explore practical techniques and lessons learned from securing WordPress websites. The presentation focuses on building a multilayered security strategy that reduces vulnerabilities and strengthens protection against unauthorized access.
Topics covered include:
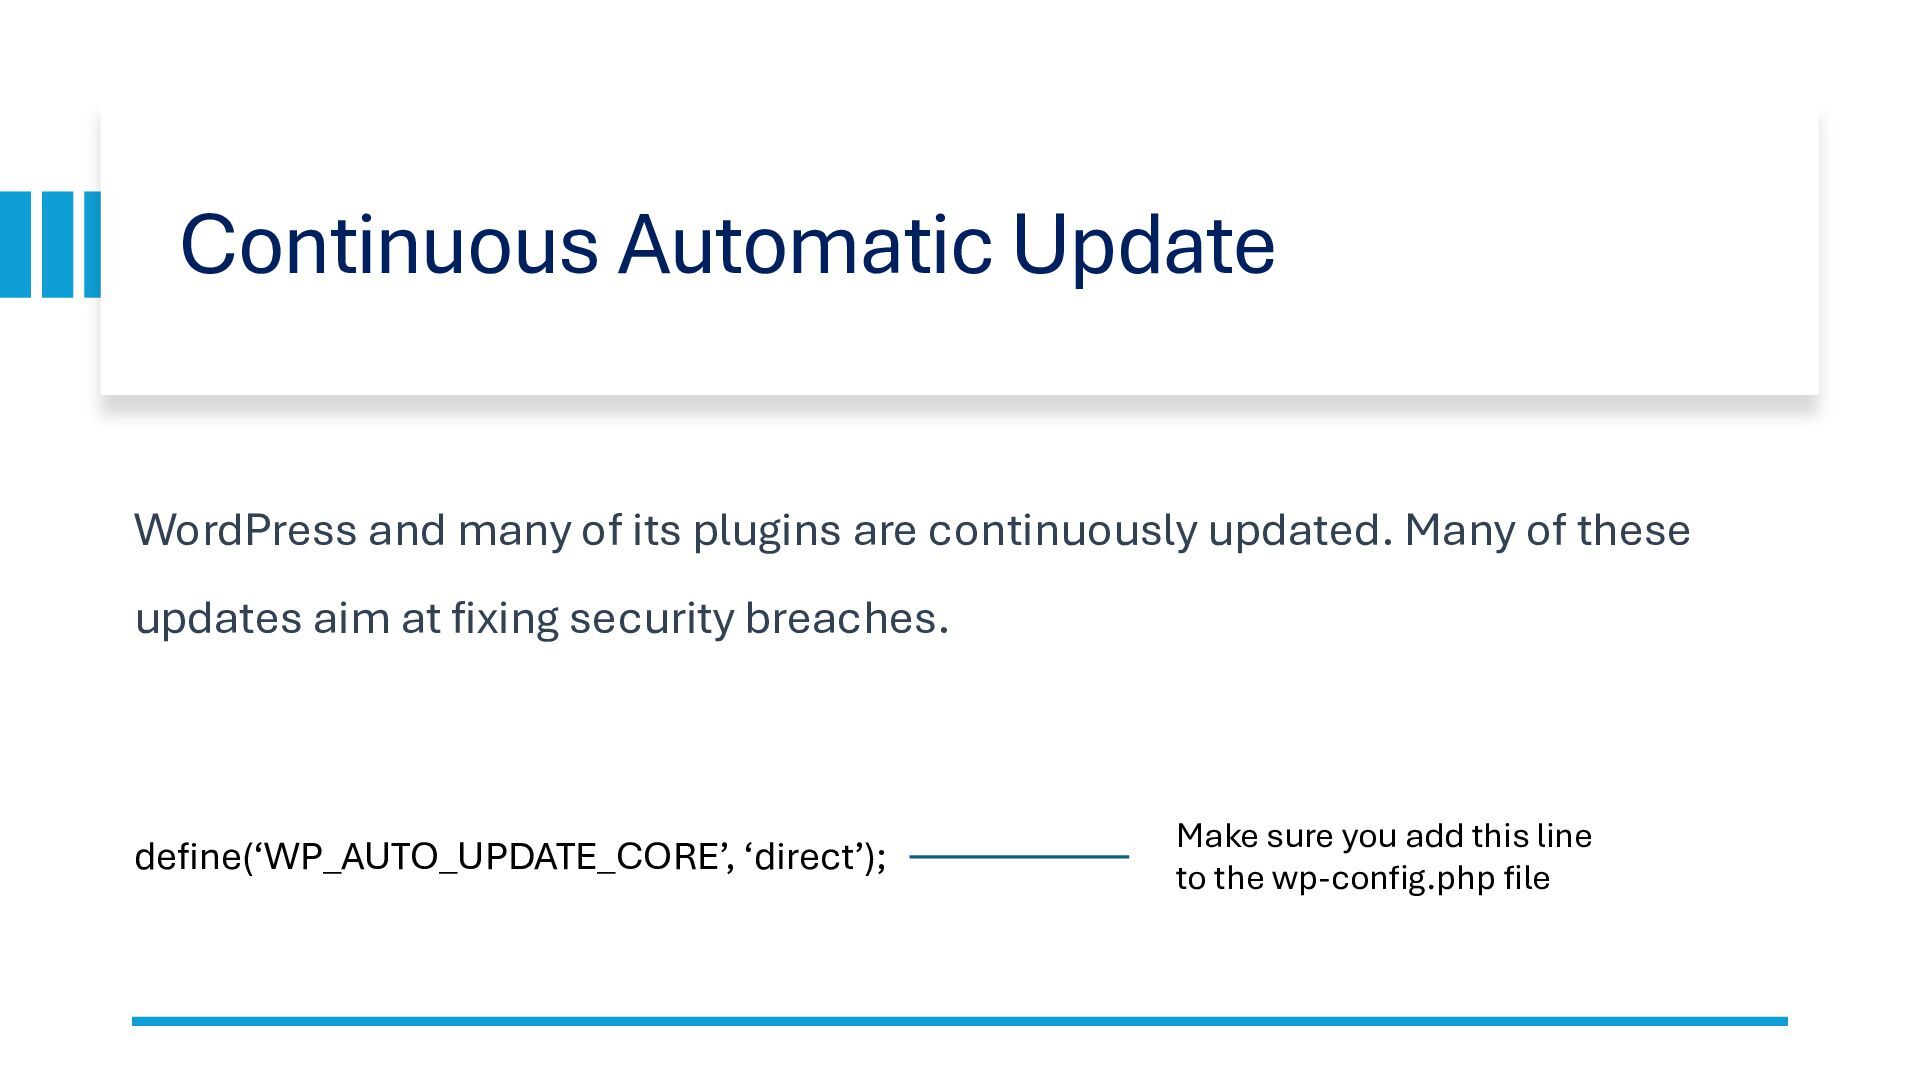
+ Hardening WordPress installations and applying security updates.
+ Securing file and directory ownership and permissions.
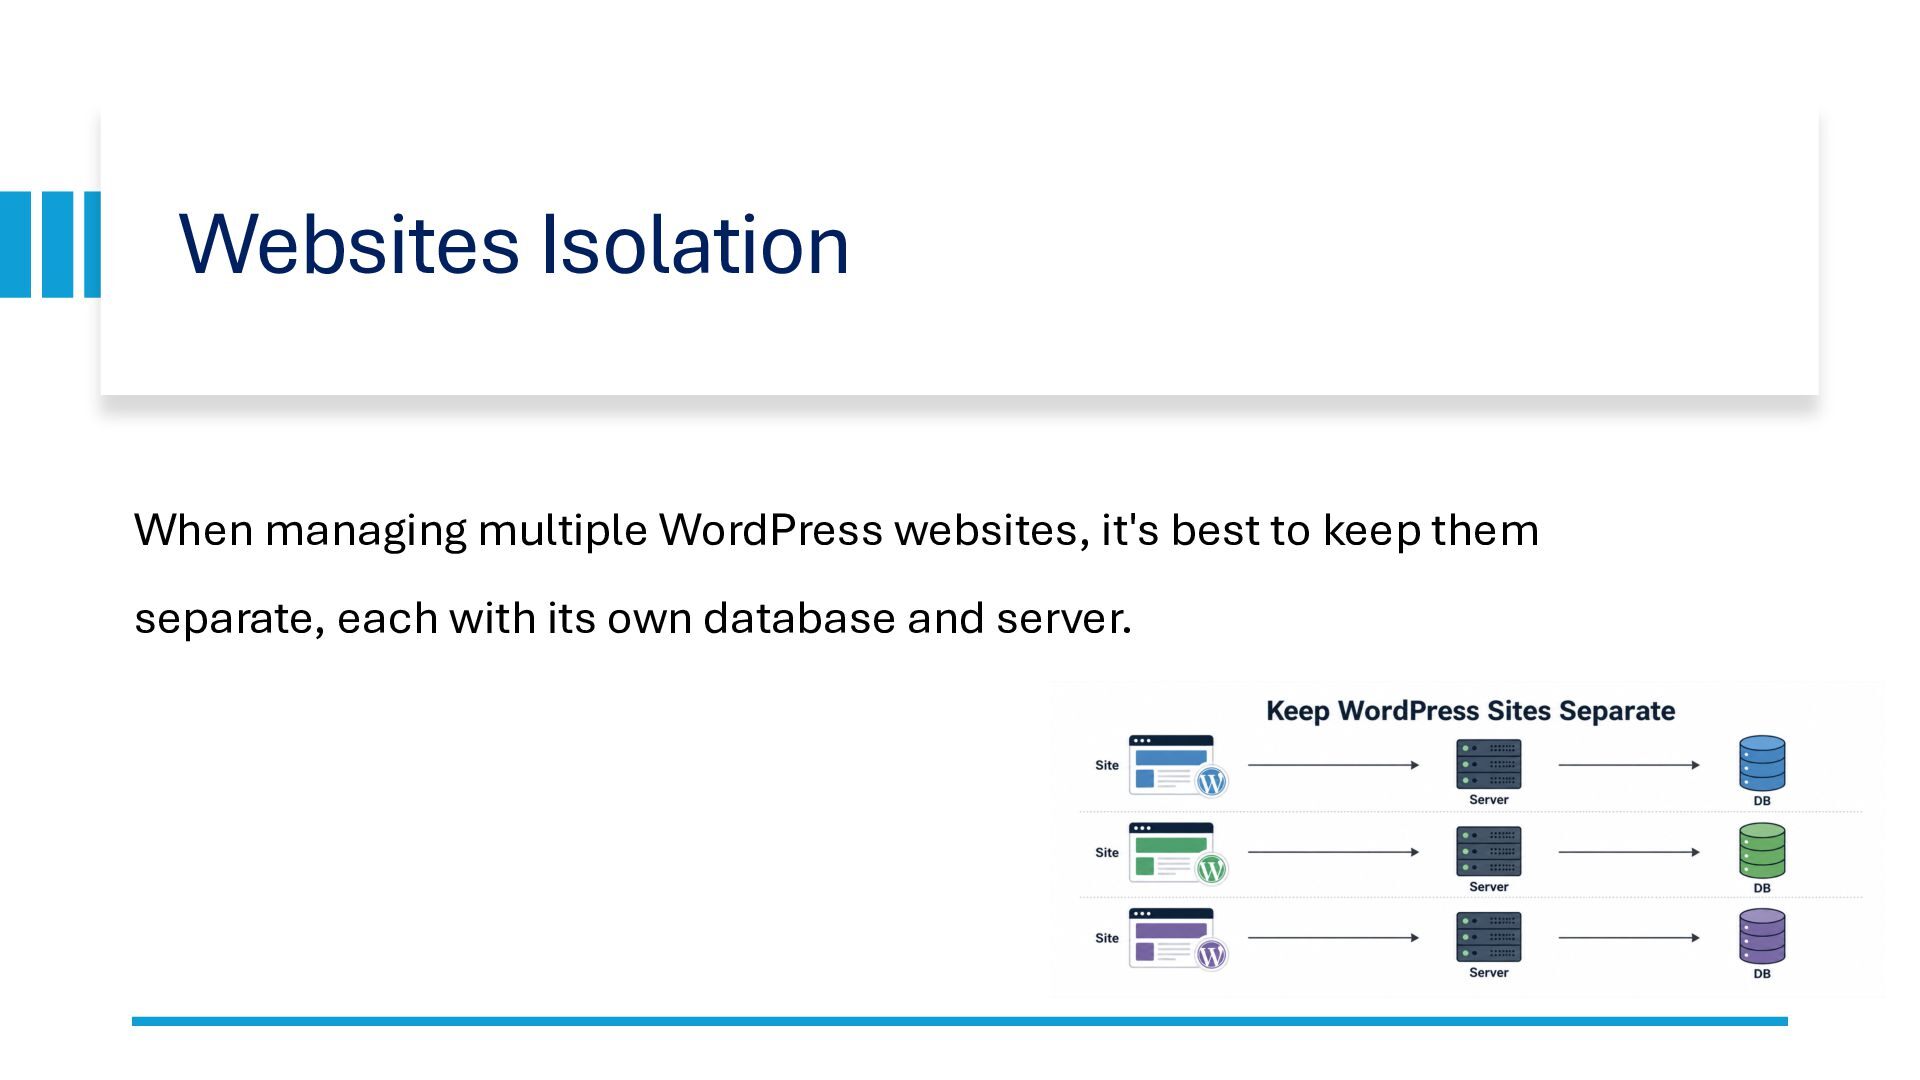
+ Isolating WordPress websites and their databases.
+ Reducing unnecessary plugins, themes, and exposed services.
+ Strengthening authentication with two-factor authentication (2FA).
+ Configuring firewalls and restricting administrative access.
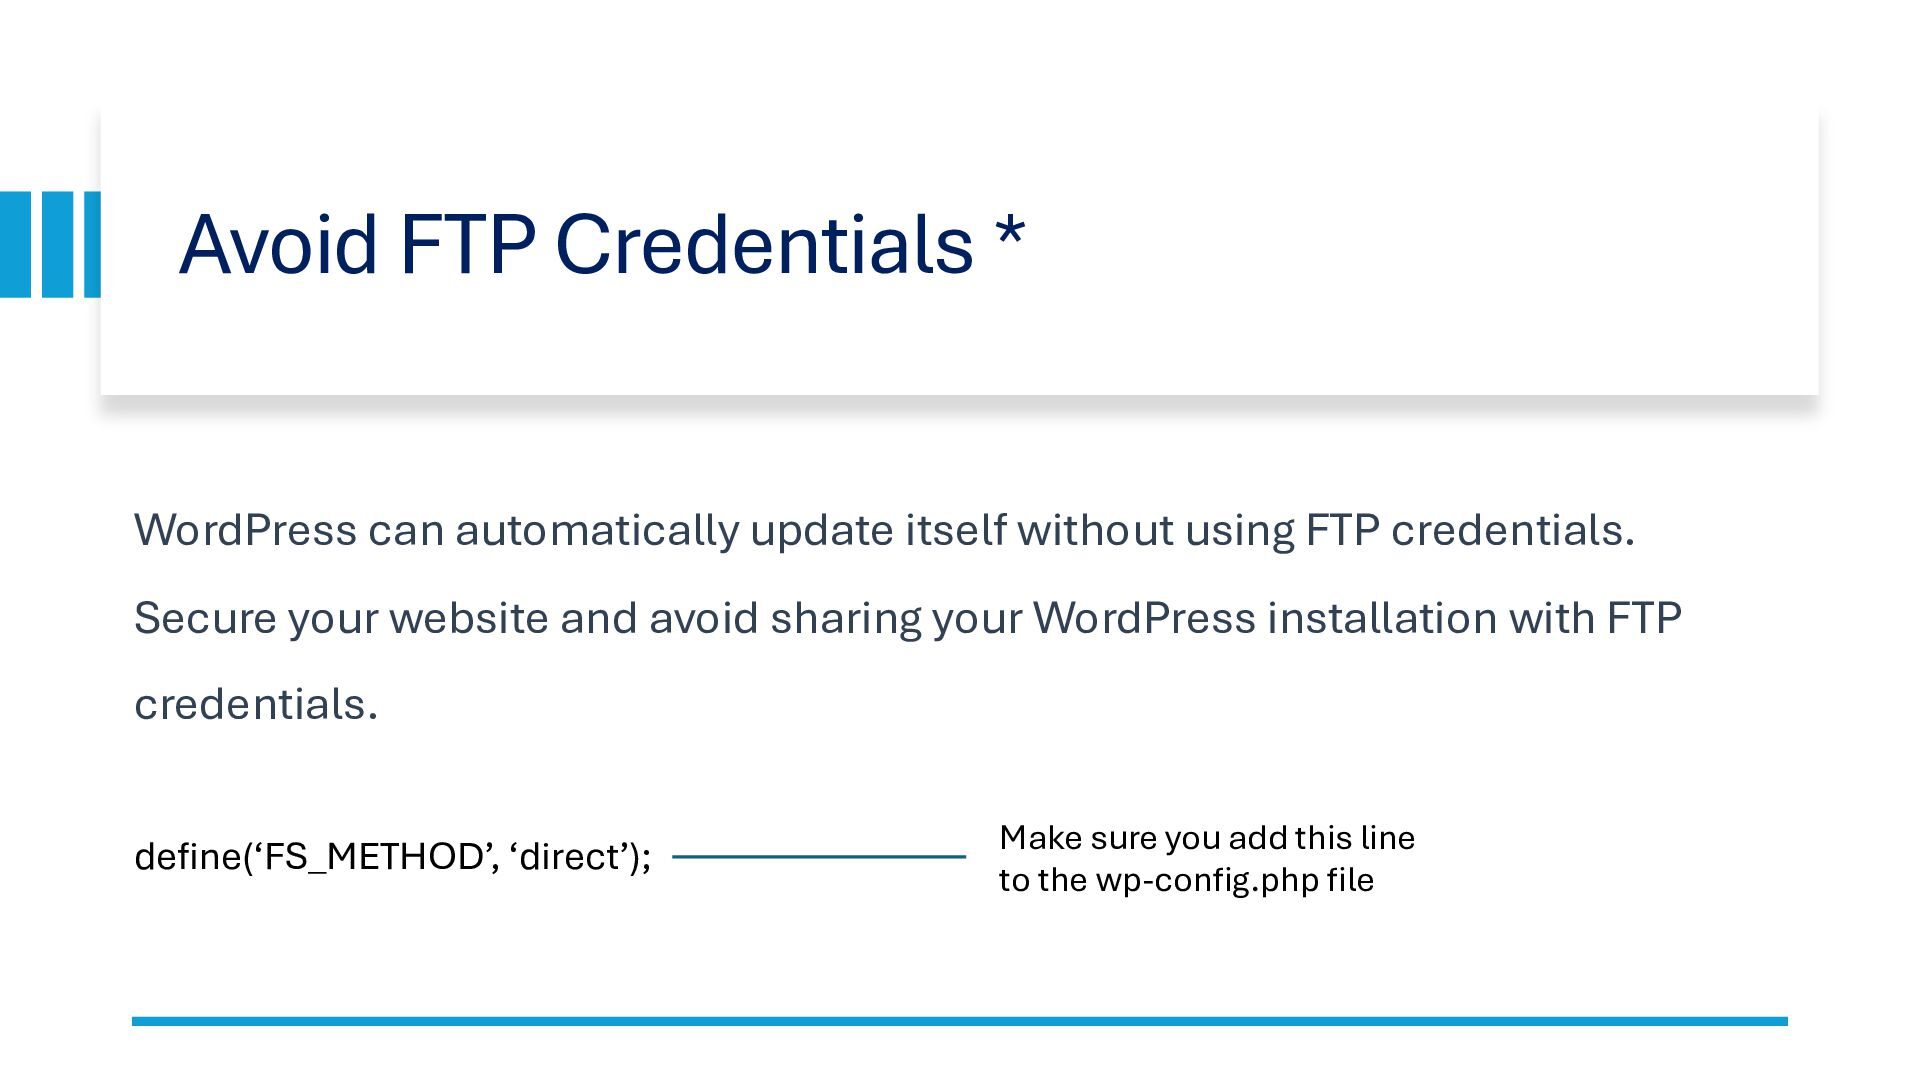
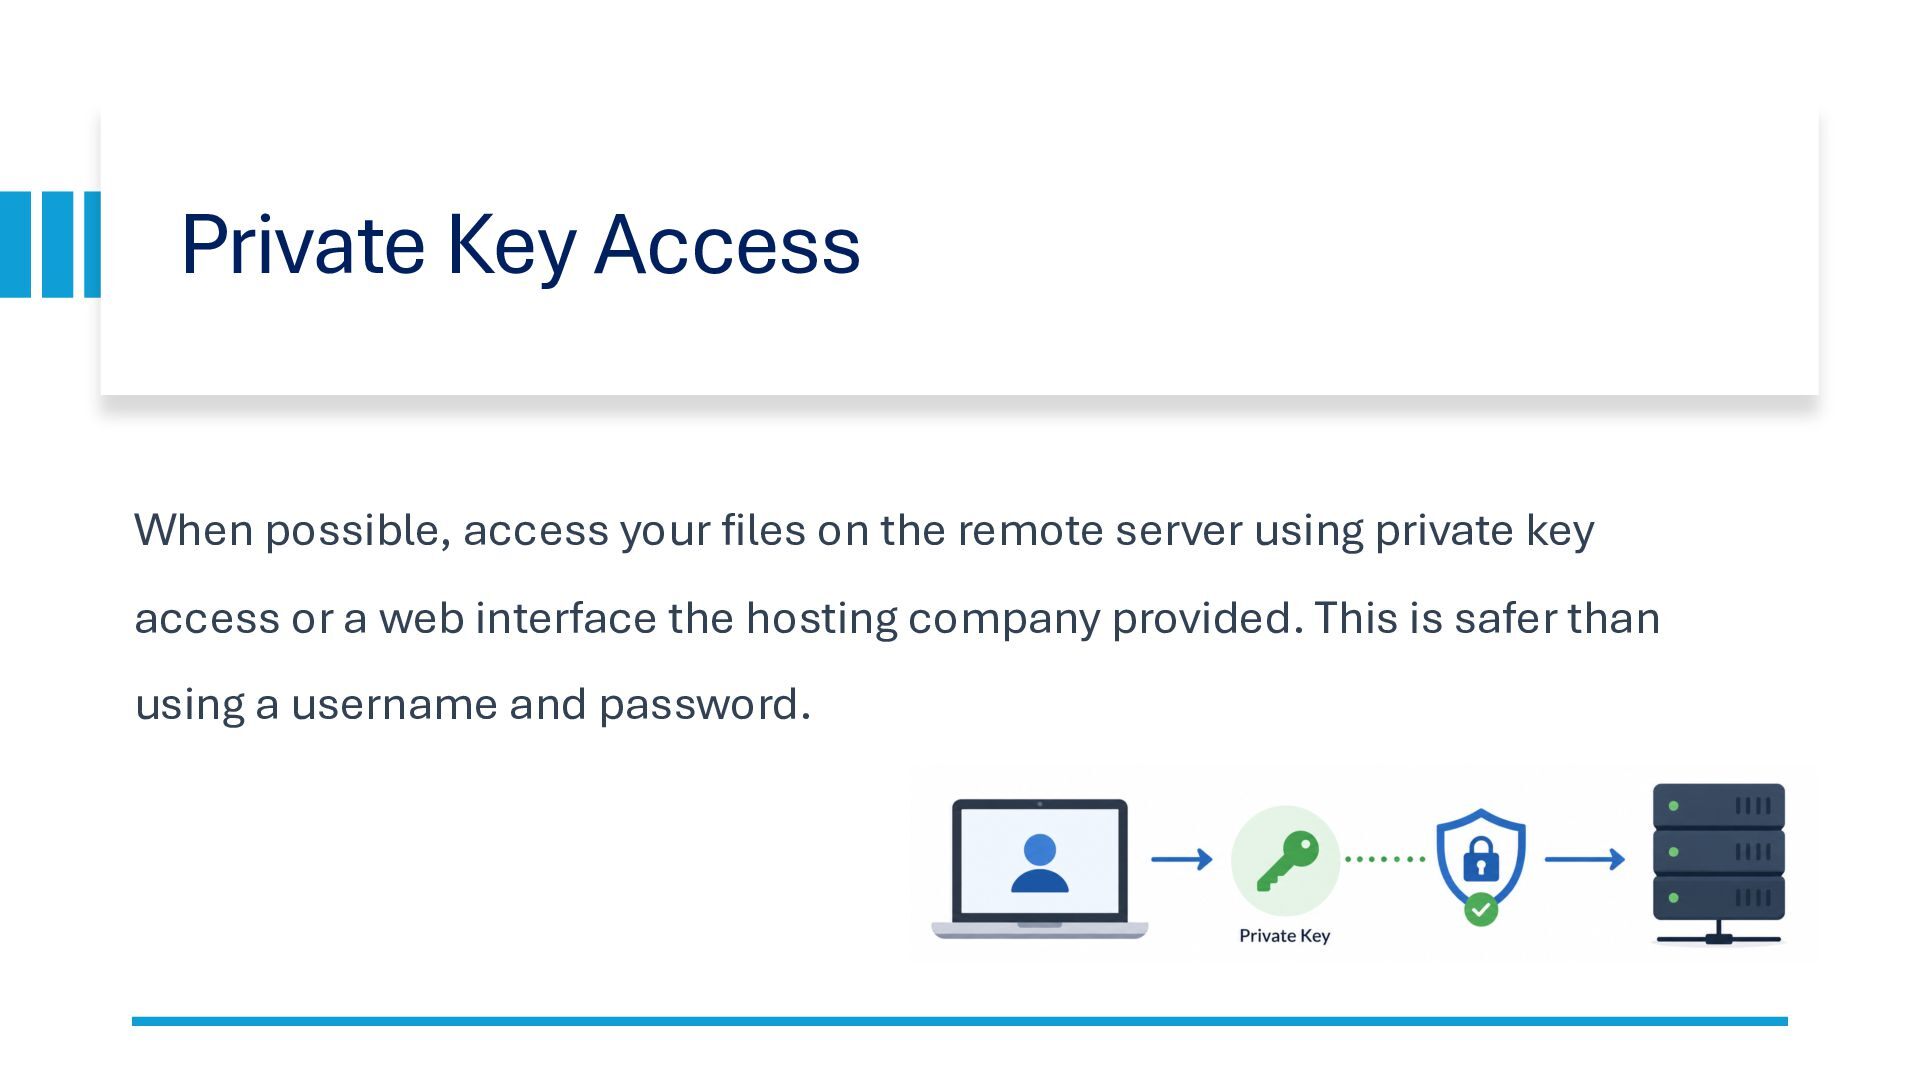
+ Avoiding unnecessary FTP credentials and using secure server access.
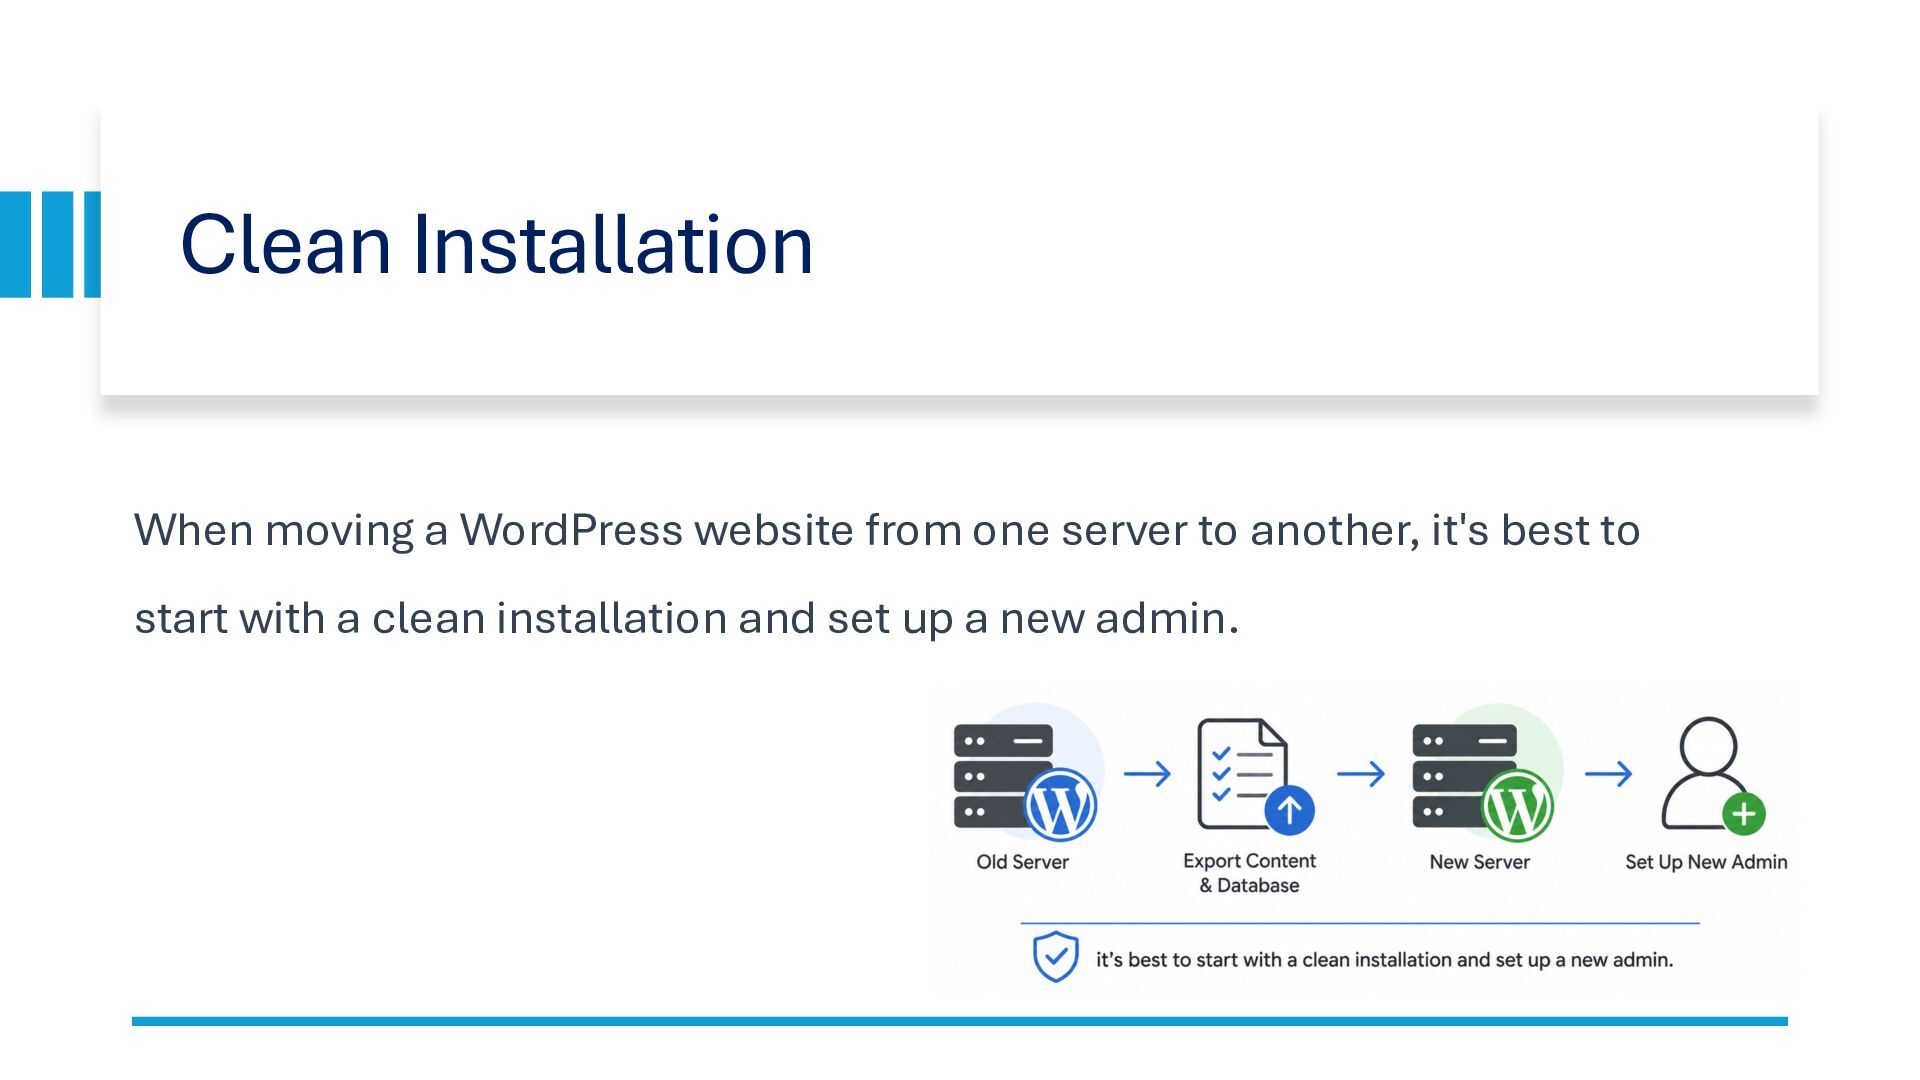
+ Migrating and recovering WordPress installations without carrying over potential backdoors.
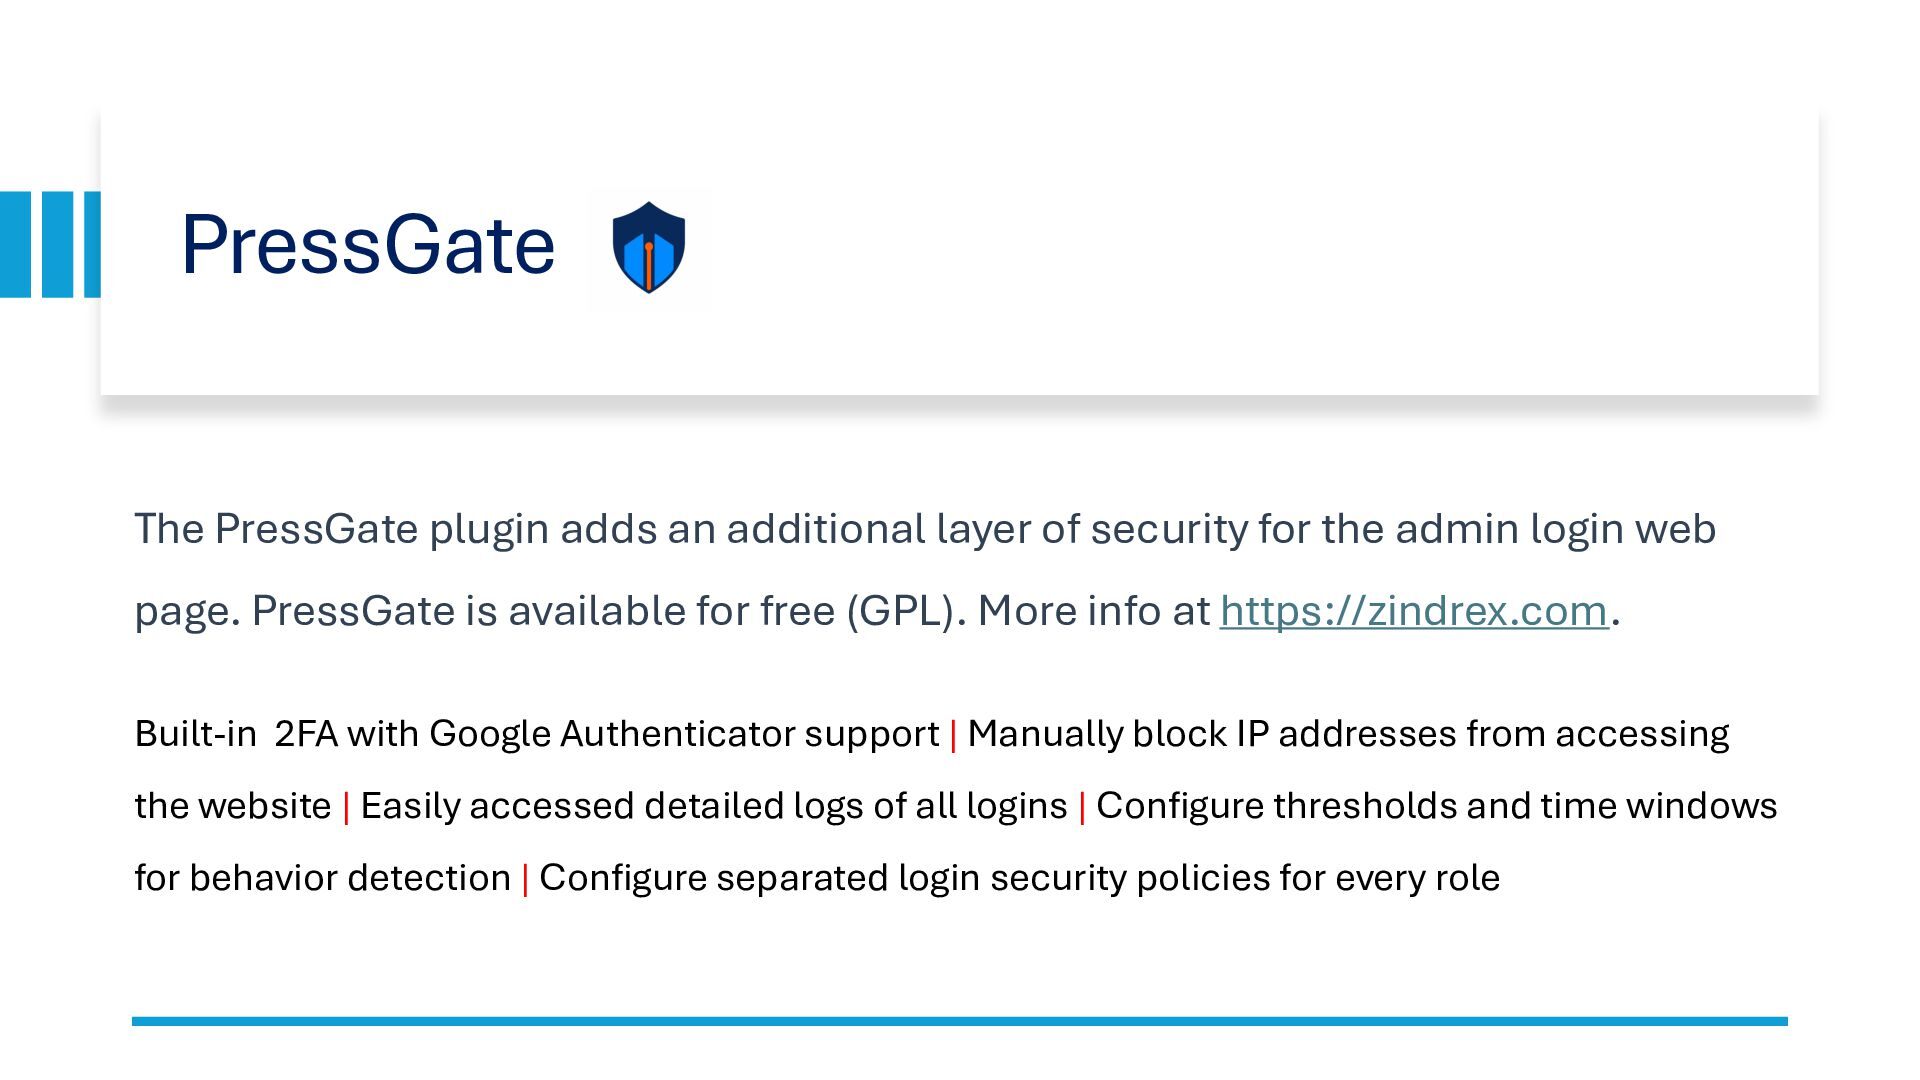
+ Use PressGate, a free WordPress plugin, to strengthen login.
PressGate provides an additional layer of security with TOTP-based authentication, IP blocking, login monitoring, behavior detection, and role-specific security policies. You can install it for free. More info at https://zindrex.com/pressgate
The central message: WordPress security is an ongoing operational discipline, not a one-time configuration. A WAF is an important defense, but effective protection requires multiple complementary security layers. These slides offer practical recommendations for WordPress developers, website administrators, and security professionals looking to build more resilient WordPress websites.
PressGate: https://zindrex.com/pressgate
Blog Post: https://lifemichael.com/en/sharing-my-experience-at-wordcamp-sofia-2026/

 lifemichael
 yoshimura_datam
 minorun365
 junjikoide
 munenick
 amixedcolor
 azukiazusa1
 wind111
 csswizardry
 rfdnxbro
 ota1022
 inesmontani
 mtmtfactory01
 techseoconnect
 lynnandtonic
 kimpetersen
 bkeepers
 tammyeverts
 jdejongh
 irinanazarova
 nikkihalliwell
 ammeep
 sstephenson
 reverentgeek