Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Google IO 2019 recap Security
Search
LINE Developers
May 22, 2019
Technology
1.9k
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Google IO 2019 recap Security
Google I/O 2019 Recap at LINE
コキチーズ
LINE Developers
May 22, 2019
More Decks by LINE Developers
See All by LINE Developers
LINEスタンプのSREing事例集:大きなスパイクアクセスを捌くためのSREing
line_developers
3
2.6k
Java 21 Overview
line_developers
6
1.4k
Code Review Challenge: An example of a solution
line_developers
1
1.7k
KARTEのAPIサーバ化
line_developers
1
660
著作権とは何か?〜初歩的概念から権利利用法、侵害要件まで
line_developers
5
2.4k
生成AIと著作権 〜生成AIによって生じる著作権関連の課題と対処
line_developers
3
2.6k
マイクロサービスにおけるBFFアーキテクチャでのモジュラモノリスの導入
line_developers
9
4.2k
A/B Testing at LINE NEWS
line_developers
3
1.2k
LINEのサポートバージョンの考え方
line_developers
2
1.6k
Other Decks in Technology
See All in Technology
メルペイ 会計システム概要と歴史
mewuto
0
210
AI時代だからこそ推したい!Gitコマンド再入門
munakata
0
180
オンラインゲームのシステム全体像 - コロプラ 2026年度 新卒研修
colopl
0
1.1k
ゲームのリアルタイム通信から見た QUIC と MoQ
segadevtech
0
110
大型犬好きによるPugの紹介
yamanoku
1
150
AIがコードを書く時代に、エンジニアは何で自分の価値を証明するのか / In an era where AI writes code how do engineers prove their value
carta_engineering
3
860
全PRの83%が AIレビューだけでマージできるようになった開発組織は その後どうなったか @2026/10
athug
0
140
Loop Engineering これくらいでいい
mikanichinose
0
230
無理せず続ける、子育てエンジニアの学び
codmoninc
PRO
0
710
「事実」を「計測」して、「解釈」する 〜AWS Lambdaのメモリ最適解の見つけ方〜
maimyyym
0
140
会社説明資料
persolserverworks
0
9.7k
AI駆動開発の時代になったのでトヨタ生産方式から見直す
terurou
7
5.8k
Featured
See All Featured
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
Balancing Empowerment & Direction
lara
6
1.3k
Groundhog Day: Seeking Process in Gaming for Health
codingconduct
0
400
How STYLIGHT went responsive
nonsquared
100
6.3k
The AI Revolution Will Not Be Monopolized: How open-source beats economies of scale, even for LLMs
inesmontani
PRO
3
3.8k
The Curse of the Amulet
leimatthew05
3
15k
個人開発の失敗を避けるイケてる考え方 / tips for indie hackers
panda_program
123
22k
Dealing with People You Can't Stand - Big Design 2015
cassininazir
367
27k
The agentic SEO stack - context over prompts
schlessera
0
970
KATA
mclloyd
PRO
35
16k
Are puppies a ranking factor?
jonoalderson
2
4k
AI Search: Where Are We & What Can We Do About It?
aleyda
0
8.1k
Transcript
Google I/O 2019 recap Security コキチーズ@k2wanko Google I/O 2019 Recap
at LINE Slideは DarkTheme セキュリティエンジニア
コキチーズ@k2wanko セキュリティエンジニア 会社のサービスの脆弱性探したり Bug Bountyを運営したりしてる WebとAndroidとGoとGCPとFirebaseとかが好き Splatoon 2のウデマエはX2300~2500くらい PUBGも好きです。
今年は セキュリティとプライバシーを 強調していた (とコキチーズは思った)
Incognito mode
Incognito mode
Android
Platform - Encryption - Qからはハードウェアアクセラレーションがサポートされないデバイスでも ストレージを暗号化する - Adiantumで遅くならないようにしてる - TLS1.3がデフォルトで有効
- Project Mainline - OSのコンポーネントのいくつかを Play Storeから配信するプロジェクト - WebViewとは違って、もっと低レイヤーのコンポーネントのアップデートが可能になる - Hardening - ソフトウェアコーデックの Sandbox - アドレス空間のランダム化 (ASLR) - https://security.googleblog.com/2019/05/queue-hardening-enhancements.html - App Signing by Google Play - 弱い暗号鍵はGoogleが強い暗号鍵にして署名してくれるようになる
Privacy Checklist https://developer.android.com/preview/privacy/checklist - Scoped storage - More user control
over location permissions - Background activity starts - Non-resettable hardware identifiers - Permission for wireless scanning
Scoped storage - /sdcard へのアクセスを制限 - getExternalFilesDir() で読み書きは変わらない ただし、他のアプリが作成したファイルにはアクセスできなくなる -
他のアプリが作ったファイルへのアクセスはDocumentProviderを使う - 写真、音声、動画は MediaStoreからアクセスする - EXIFへのアクセスにはACCESS_MEDIA_LOCATIONが必要
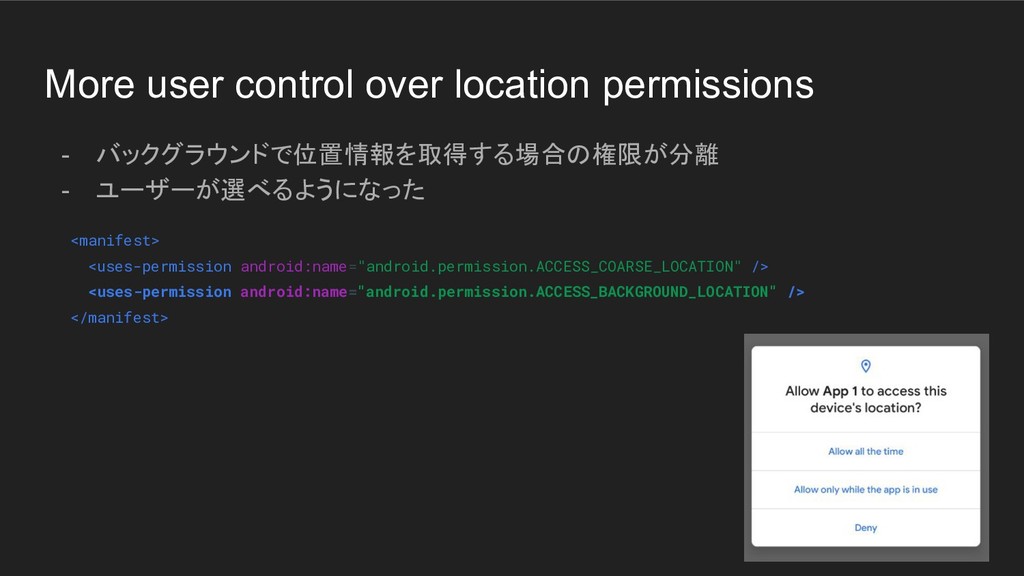
More user control over location permissions - バックグラウンドで位置情報を取得する場合の権限が分離 - ユーザーが選べるようになった
<manifest> <uses-permission android:name="android.permission.ACCESS_COARSE_LOCATION" /> <uses-permission android:name="android.permission.ACCESS_BACKGROUND_LOCATION" /> </manifest>
None
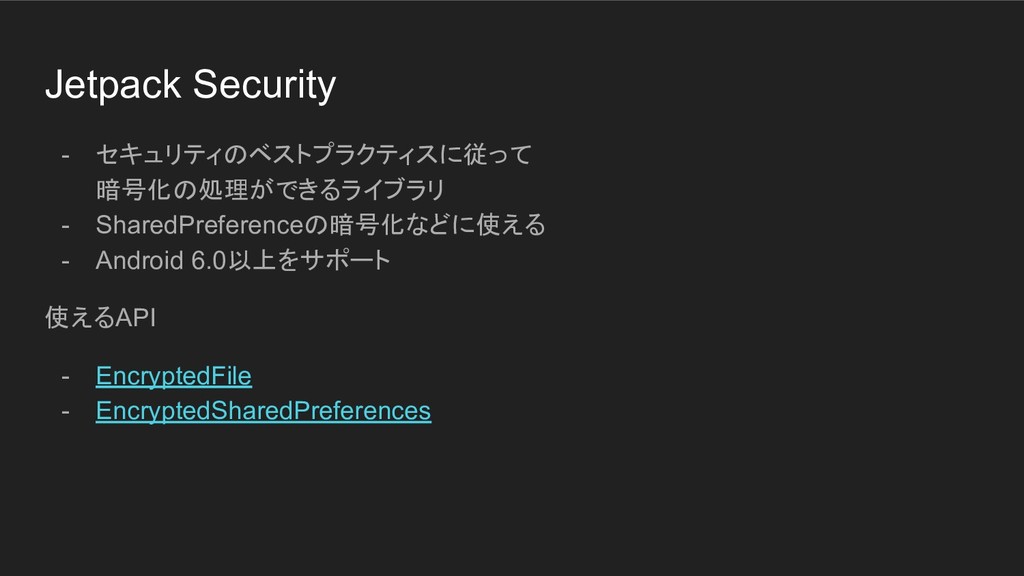
Jetpack Security - セキュリティのベストプラクティスに従って 暗号化の処理ができるライブラリ - SharedPreferenceの暗号化などに使える - Android 6.0以上をサポート
使えるAPI - EncryptedFile - EncryptedSharedPreferences
EncryptedFile String masterKeyAlias = MasterKeys.getOrCreate(MasterKeys.AES256_GCM_SPEC ); File file = new
File(context.getFilesDir(), "secret_data"); // write to the encrypted file EncryptedFile encryptedFile = EncryptedFile.Builder(file, context, masterKeyAlias, EncryptedFile.FileEncryptionScheme .AES256_GCM_HKDF_4KB ).build(); // read the encrypted file FileOutputStream encryptedOutputStream = encryptedFile.openFileOutput (); FileInputStream encryptedInputStream = encryptedFile.openFileInput();
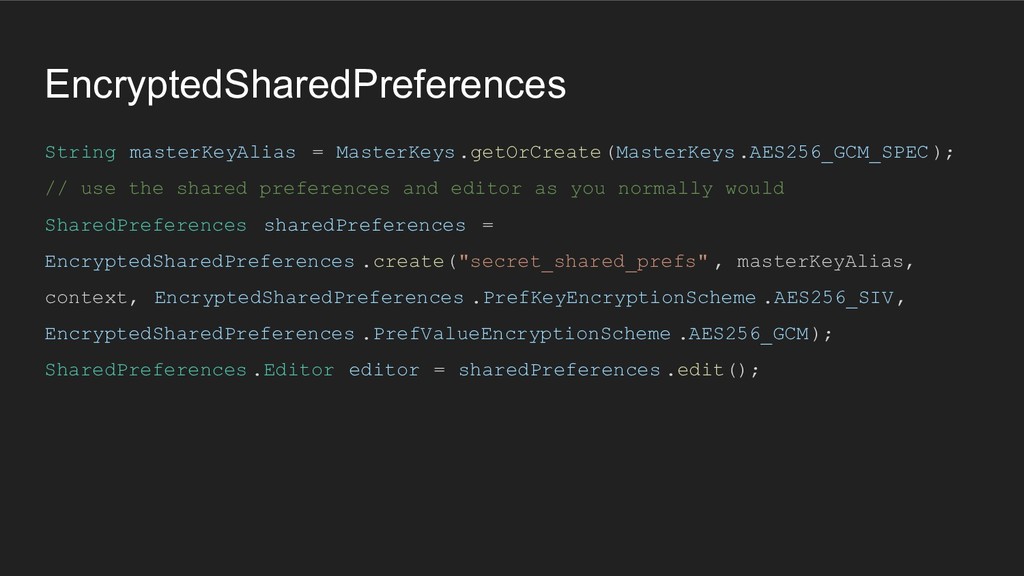
EncryptedSharedPreferences String masterKeyAlias = MasterKeys.getOrCreate(MasterKeys.AES256_GCM_SPEC ); // use the shared
preferences and editor as you normally would SharedPreferences sharedPreferences = EncryptedSharedPreferences .create("secret_shared_prefs" , masterKeyAlias, context, EncryptedSharedPreferences .PrefKeyEncryptionScheme .AES256_SIV, EncryptedSharedPreferences .PrefValueEncryptionScheme .AES256_GCM); SharedPreferences .Editor editor = sharedPreferences .edit();
Web
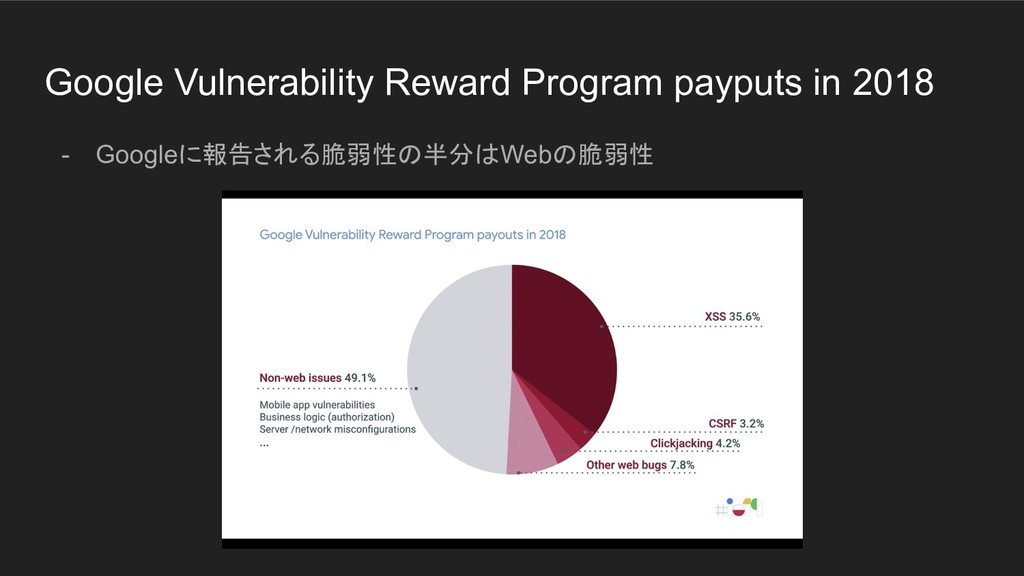
Google Vulnerability Reward Program payputs in 2018 - Googleに報告される脆弱性の半分はWebの脆弱性
Content Security Policy (CSP) - サイトが読み込めるリソースをホワイトリストできめ細やかに設定できる - Response Headerに「Content-Security-Policy: <policy>」と書くと有効にできる。
- 「Content-Security-Policy-Report-Only」でリソースを実際にブロックせず エラーだけ確認することもできる。
nonce & strict-dynamic based CSP - Googleは nonceとstrict-dynamicを使ったCSPを推奨している - nonceはランダムな値
Content-Security-Policy: script-src ‘nonce-random123’ - nonce属性が一致しない場合は実行されない <script>alert(‘xss’)</script> // block! <script nonce=”random123”>alert(‘this is fine!’)</script> // run
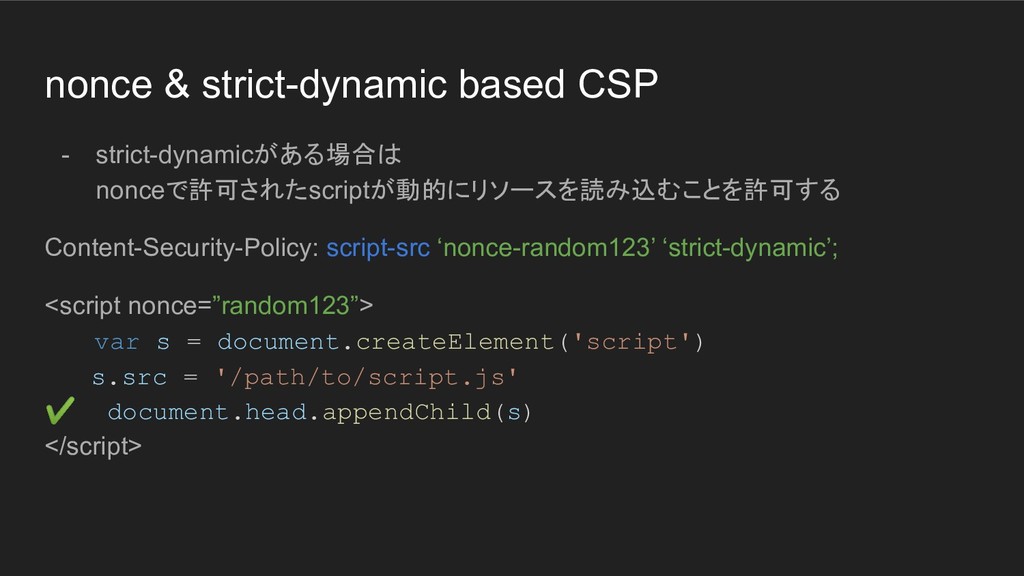
nonce & strict-dynamic based CSP - strict-dynamicがある場合は nonceで許可されたscriptが動的にリソースを読み込むことを許可する Content-Security-Policy: script-src
‘nonce-random123’ ‘strict-dynamic’; <script nonce=”random123”> var s = document.createElement('script') s.src = '/path/to/script.js' ✔ document.head.appendChild(s) </script>
CSP hashes - 静的ファイルの場合はハッシュを埋め込んで許可することもできる Content-Security-Policy: script-src ‘sha256-...’ ‘strict-dynamic’;
Detailed guide https://csp.withgoogle.com/docs/index.html
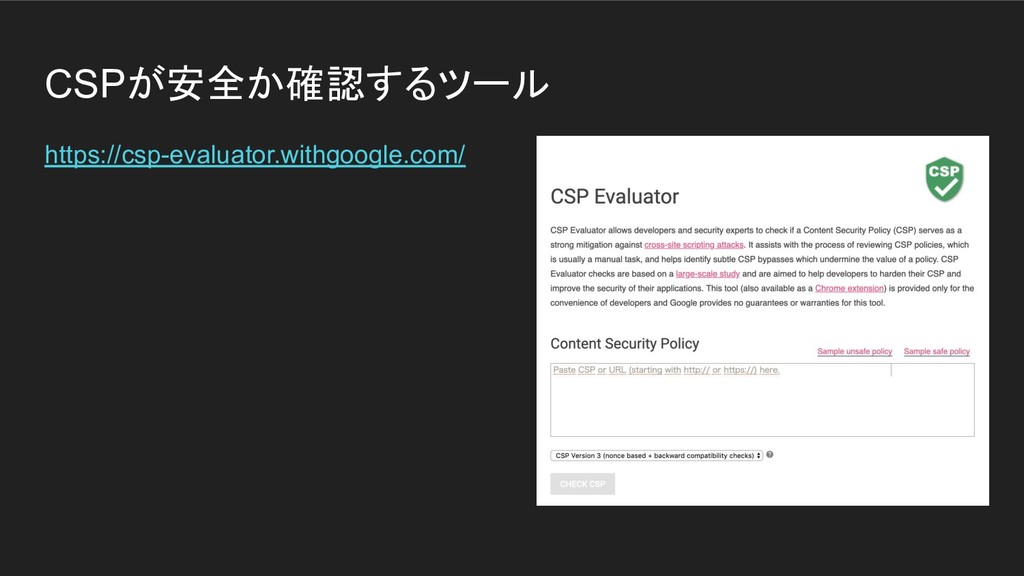
CSPが安全か確認するツール https://csp-evaluator.withgoogle.com/
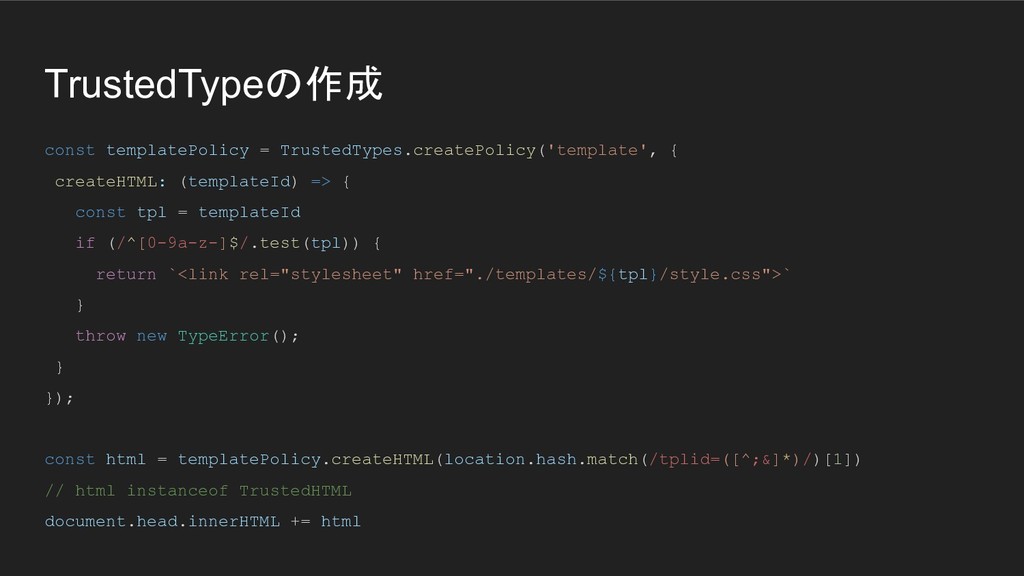
Trusted Type - CSPでは防げないDOM Based XSSを防ぐためのAPI - innerHTMLやlocation.hrefなど危険なAPIに値を入れるときは stringではなく信頼できる型に変換して入力するようにする
TrustedTypeの作成 const templatePolicy = TrustedTypes.createPolicy('template', { createHTML: (templateId) => {
const tpl = templateId if (/^[0-9a-z-]$/.test(tpl)) { return `<link rel="stylesheet" href="./templates/${tpl}/style.css">` } throw new TypeError(); } }); const html = templatePolicy.createHTML(location.hash.match(/tplid=([^;&]*)/)[1]) // html instanceof TrustedHTML document.head.innerHTML += html
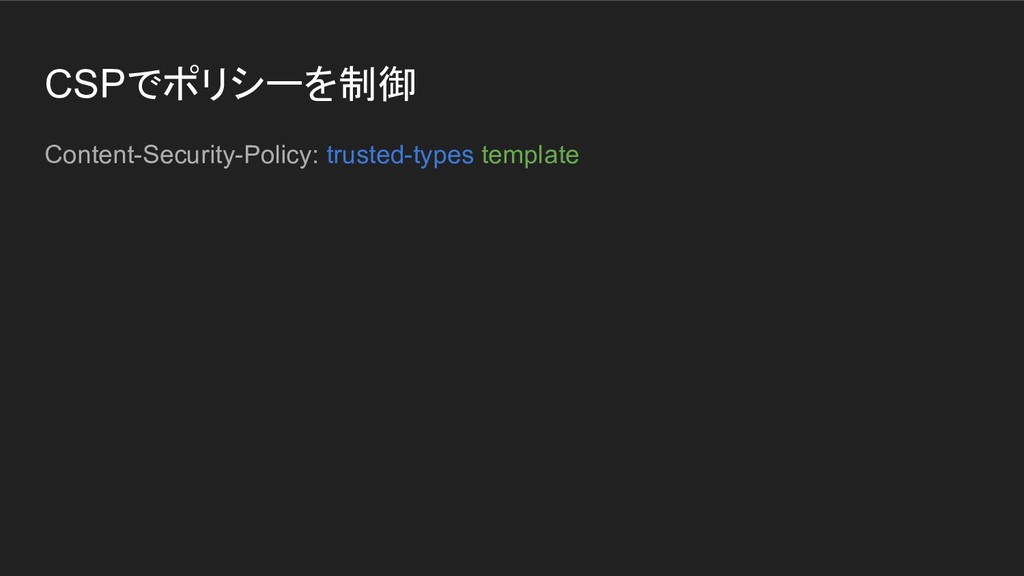
CSPでポリシーを制御 Content-Security-Policy: trusted-types template
Trusted Typeのpolyfilled https://github.com/WICG/trusted-types
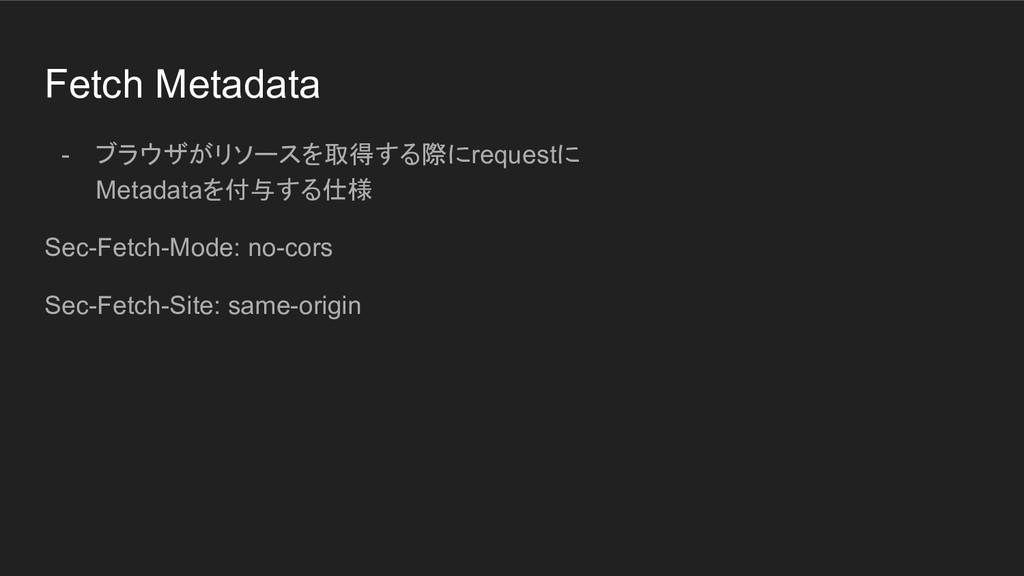
Fetch Metadata - ブラウザがリソースを取得する際にrequestに Metadataを付与する仕様 Sec-Fetch-Mode: no-cors Sec-Fetch-Site: same-origin
Cross-Origin-Opener-Policy - window.openの挙動についての仕様 - Cross-Origin-Opener-Policyヘッダーをつけて same originやsame siteに制限できる Cross-Origin-Opener-Policy: same-origin
No Security No Life @k2wanko


 line_developers
 mewuto
 munakata
 colopl
 segadevtech
 yamanoku
 carta_engineering
 athug
 mikanichinose
 codmoninc
 maimyyym
 persolserverworks
 terurou
 eileencodes
 lara
 codingconduct
 nonsquared
 inesmontani
 leimatthew05
 panda_program
 cassininazir
 schlessera
 mclloyd
 jonoalderson
 aleyda