Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
AIの権限設定に悩んでいる話
Search
Shuma
March 19, 2026
Programming
81
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
AIの権限設定に悩んでいる話
2026/3/19(木) 第四回 唐揚げ会 発表LT
Shuma
March 19, 2026
More Decks by Shuma
See All by Shuma
信頼性の目標を誰も求めてない
shubox
0
570
DB移行、油断した瞬間に 肝が冷えた話
shubox
0
80
インフラ深掘りLT
shubox
0
81
飲食店長から_SREになった話
shubox
0
85
Ansible で Vector を導入し Slack 通知とログレベル色分けまでした話
shubox
0
75
阿部寛のホームページをSRE観点で改善出来るか考えてみた。
shubox
1
200
一日の終わりに、晩酌しながら眺めたいシステムログの世界
shubox
1
150
プロダクトがクローズした話
shubox
0
240
今も熱いもの!魂を揺さぶる戦士の儀式:マオリ族のハカ
shubox
0
380
Other Decks in Programming
See All in Programming
Rails初心者がパスキーを実装してみて大変だったこと
ktombow
0
150
Augmenting AI with the Power of Jakarta EE
ivargrimstad
0
130
[DroidKnights 2026] Workflow AX: From Auto-Documented Policies to E2E Testing
raeminkang
0
530
Performance Optimization With LLMs
xleitix
0
240
AI時代のTerminal環境を UNIX哲学で設計・運用する
yasunori0418
1
340
FactoryBotをやめればRSpecは速くなるのか?
yuta_onishi_97
0
1.6k
Enforcing Your Architecture with Unit Tests in the AI Era (Swift Connection X)
steliosf
PRO
1
150
Zero-Tap Sign-In対応、結局何をすればいいの?
mitohato14
0
1.6k
Будущее локальных LLM – Алексей Голобурдин, PythoNN
sobolevn
0
110
GraphQL の onError と Nullability のこれから
quramy
0
210
Inertia Rails: The One-Person Framework with React & Friends
skryukov
0
380
S3 TablesのIcebergデータに、AIエージェントからアクセスしてみた / 20261016developersio2026joetsu-accessing-iceberg-in-s3tables-via-agent
kasacchiful
PRO
0
280
Featured
See All Featured
What does AI have to do with Human Rights?
axbom
PRO
1
2.5k
How People are Using Generative and Agentic AI to Supercharge Their Products, Projects, Services and Value Streams Today
helenjbeal
2
390
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.4k
Chasing Engaging Ingredients in Design
codingconduct
0
390
jQuery: Nuts, Bolts and Bling
dougneiner
66
8.7k
Impact Scores and Hybrid Strategies: The future of link building
tamaranovitovic
0
480
Building an army of robots
kneath
307
47k
Navigating the Design Leadership Dip - Product Design Week Design Leaders+ Conference 2024
apolaine
2
510
Practical Tips for Bootstrapping Information Extraction Pipelines
honnibal
25
2.2k
The browser strikes back
jonoalderson
0
1.9k
More Than Pixels: Becoming A User Experience Designer
marktimemedia
3
620
Templates, Plugins, & Blocks: Oh My! Creating the theme that thinks of everything
marktimemedia
31
2.9k
Transcript
1 2 3 4 5 6 >_ AIは愛を知らないが、 エンジニアは AIを知っている
〜AIの権限設定に悩んでいる話〜 NotebookLM
自己紹介 名前: Shuma 職種: SRE / インフラエンジニア 興味: @ShuShuShuBOOOx 最近うれしかったこと
IaC, 障害対応, 監視, パフォーマンス改善 大きな負荷対策の監視をしていて 同じ会社の人とかなりのトラフィックをさば いたこと。
1 2 3 4 5 6 7 8 9 10
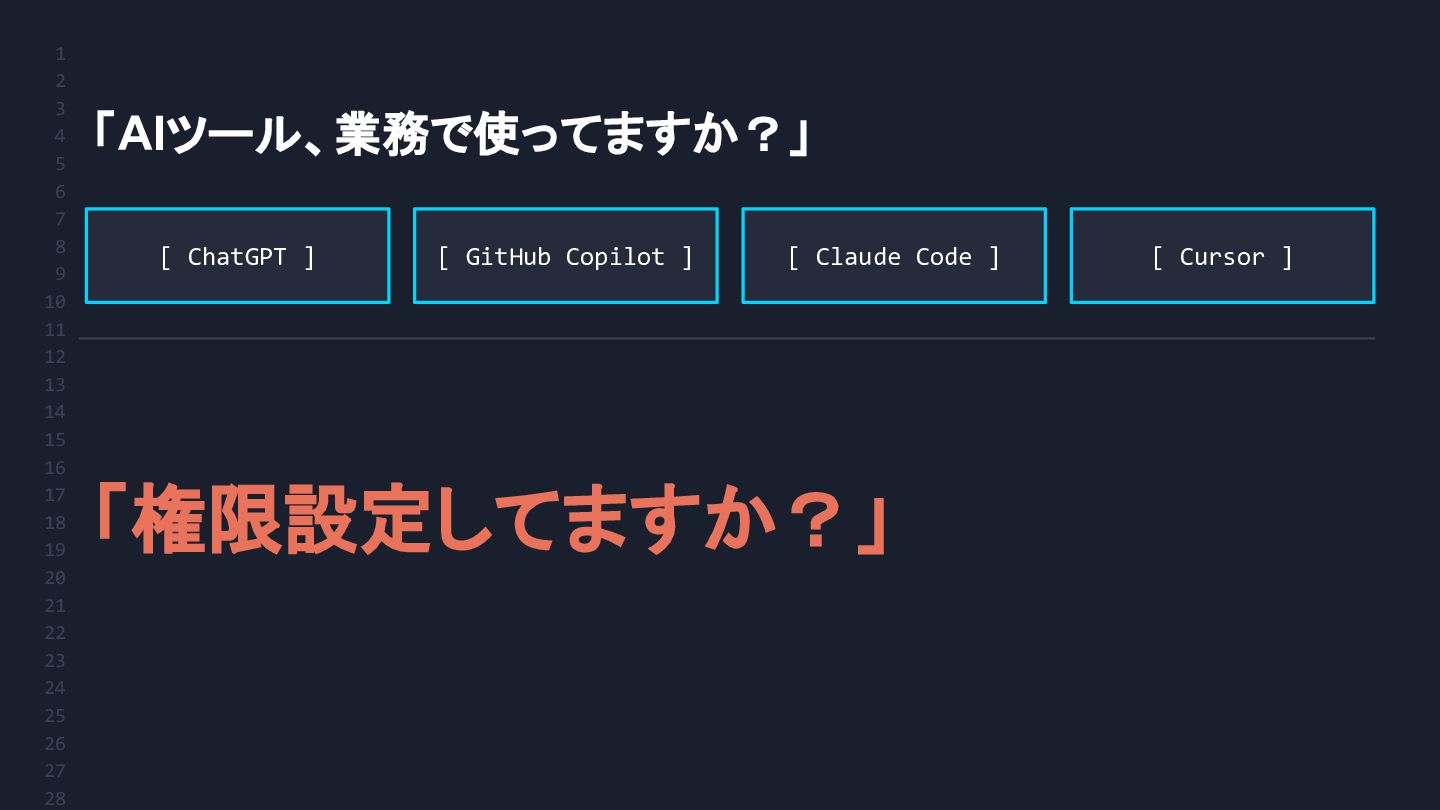
11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 「AIツール、業務で使ってますか?」 [ ChatGPT ] [ GitHub Copilot ] [ Claude Code ] [ Cursor ] 「権限設定してますか?」
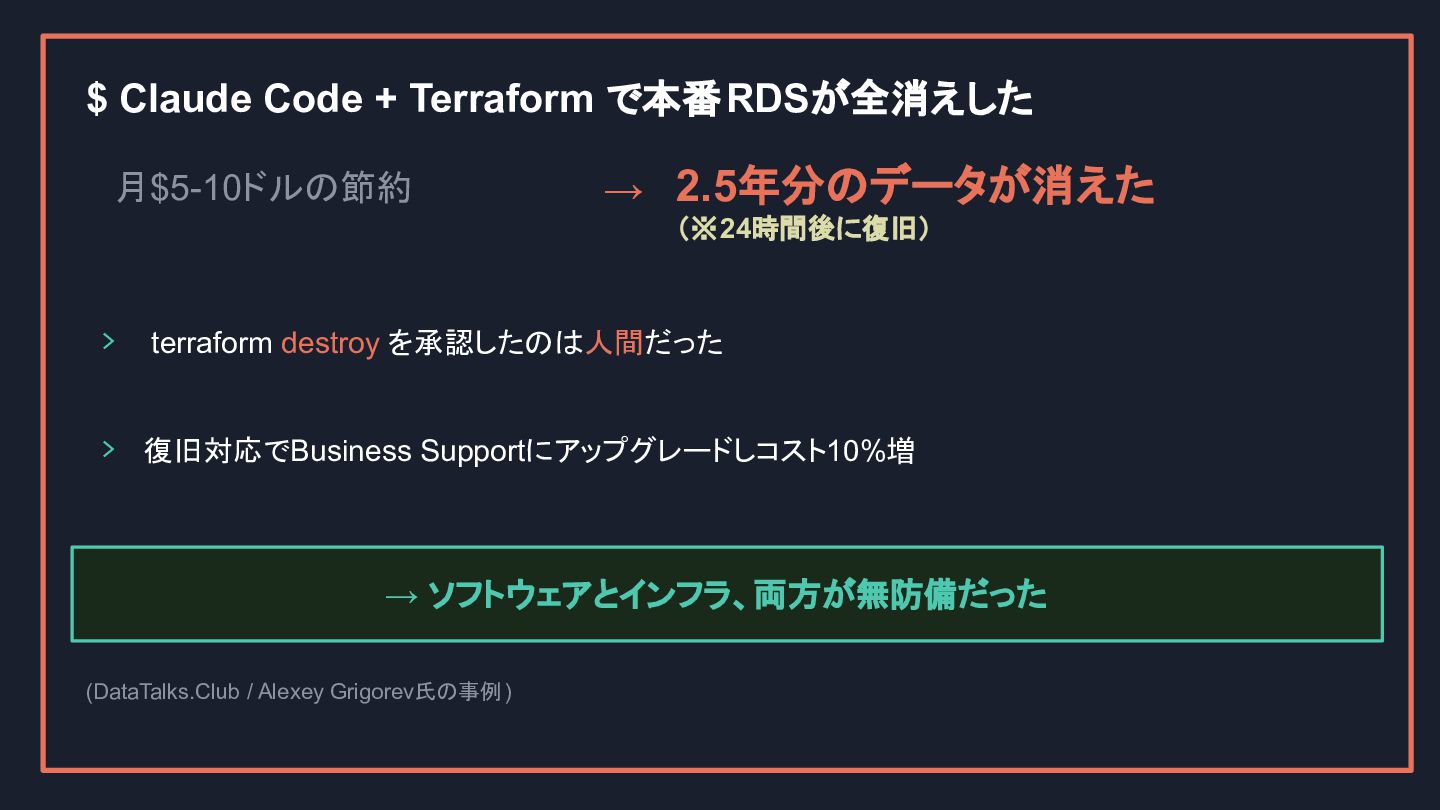
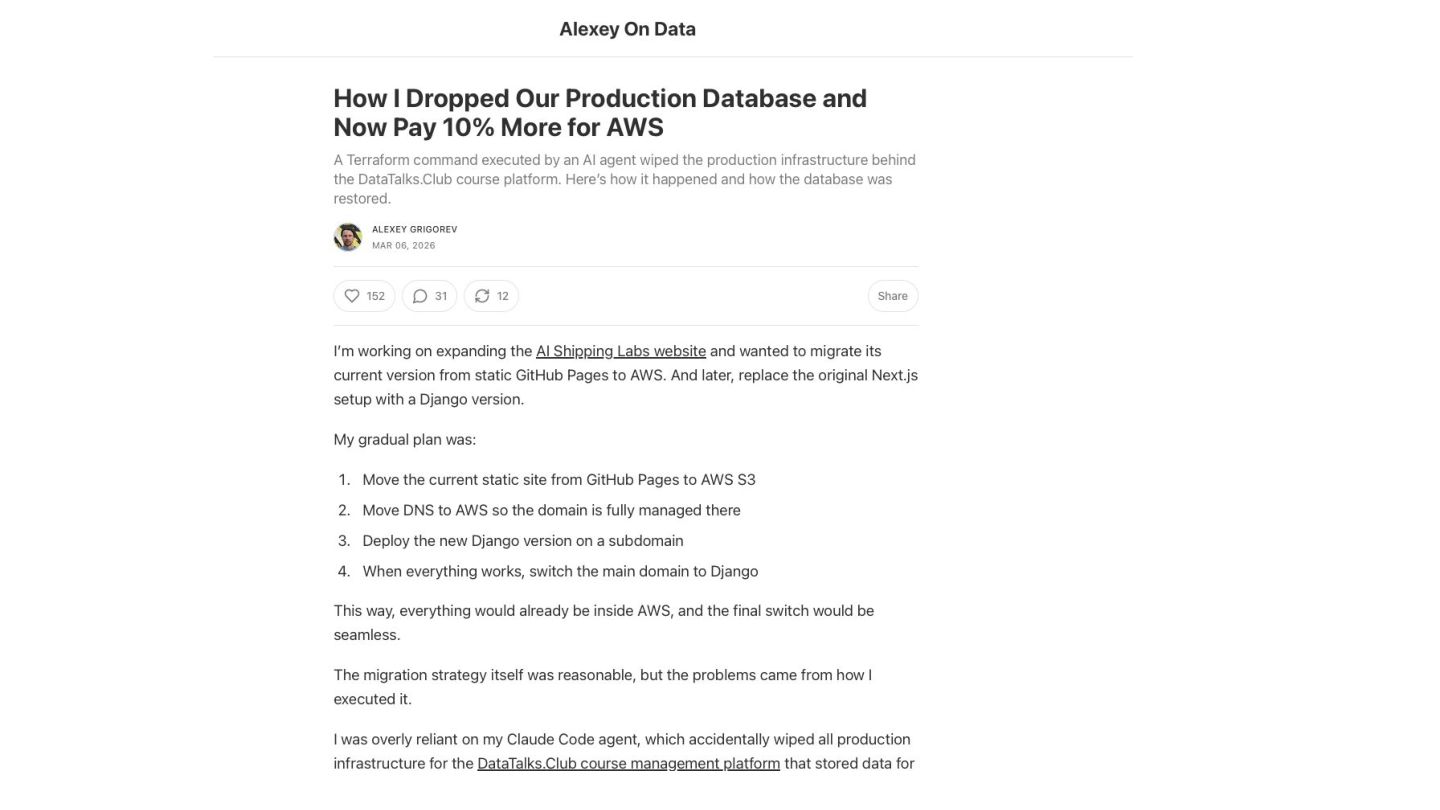
$ Claude Code + Terraform で本番RDSが全消えした 月$5-10ドルの節約 → 2.5年分のデータが消えた (※24時間後に復旧)
> terraform destroy を承認したのは人間だった > 復旧対応でBusiness Supportにアップグレードしコスト10%増 → ソフトウェアとインフラ、両方が無防備だった (DataTalks.Club / Alexey Grigorev氏の事例)
None
settings.json 1 2 3 4 5 6 7 8 9
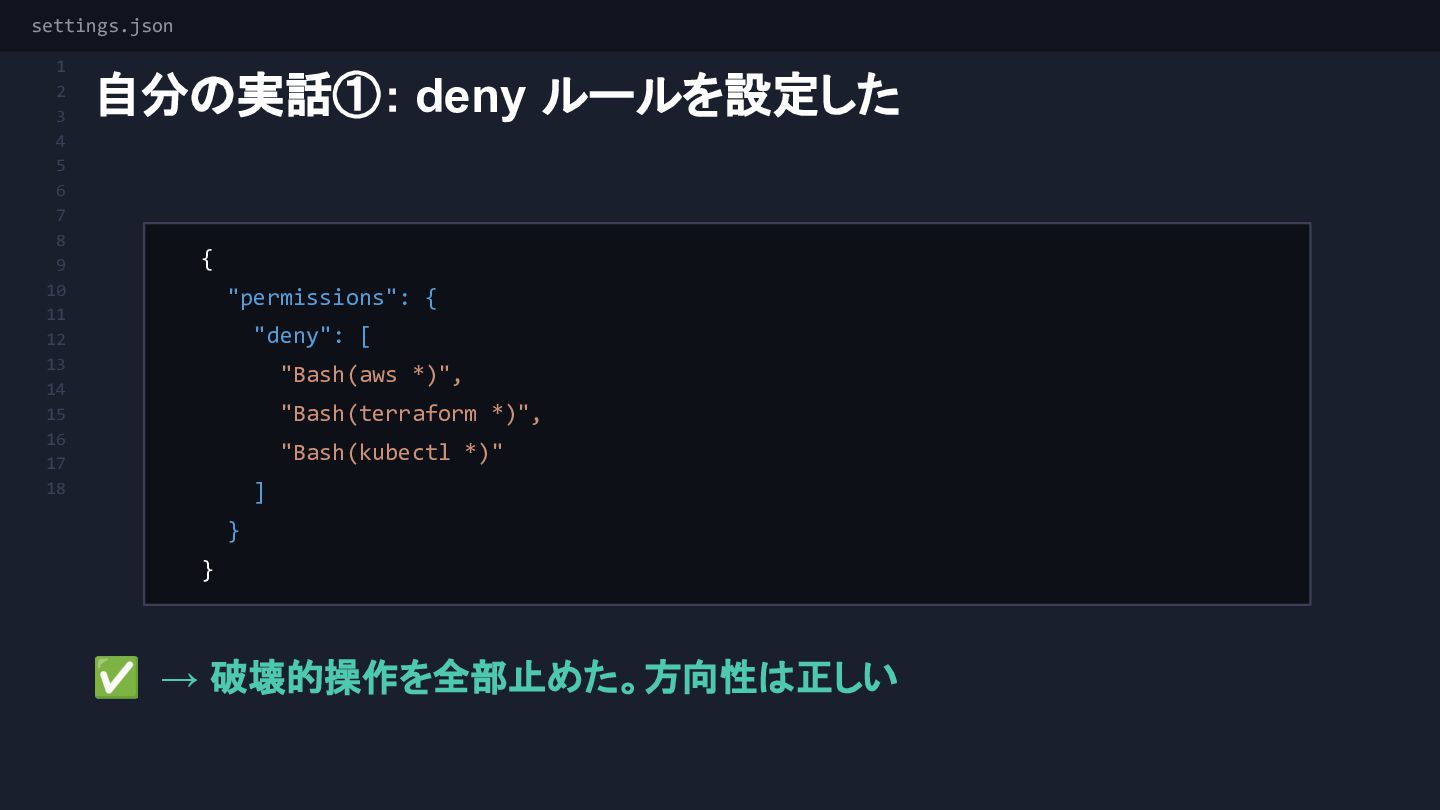
10 11 12 13 14 15 16 17 18 自分の実話①: deny ルールを設定した { "permissions": { "deny": [ "Bash(aws *)", "Bash(terraform *)", "Bash(kubectl *)" ] } } ✅ → 破壊的操作を全部止めた。方向性は正しい
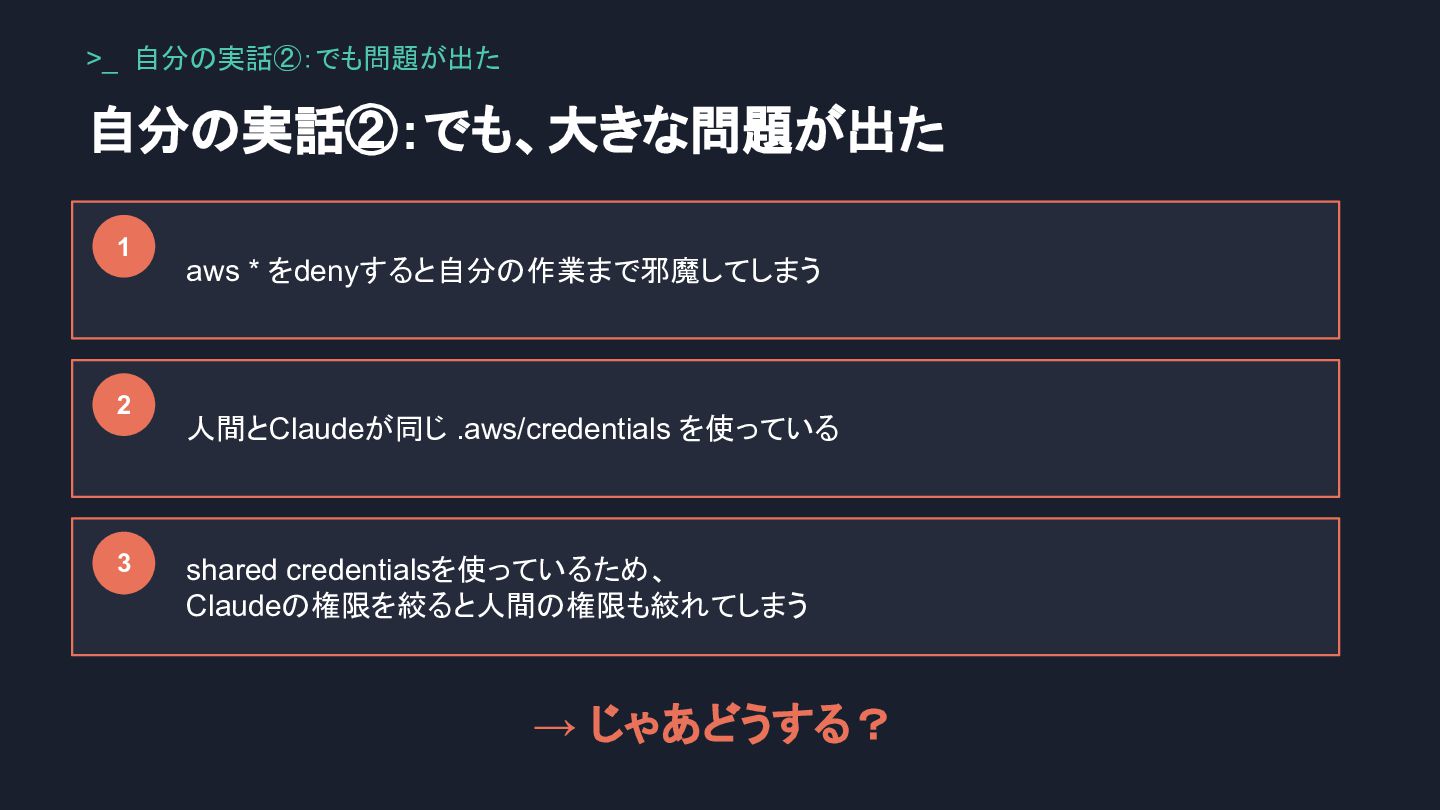
>_ 自分の実話②:でも問題が出た 自分の実話②:でも、大きな問題が出た 1 aws * をdenyすると自分の作業まで邪魔してしまう 2 人間とClaudeが同じ .aws/credentials
を使っている 3 shared credentialsを使っているため、 Claudeの権限を絞ると人間の権限も絞れてしまう → じゃあどうする?
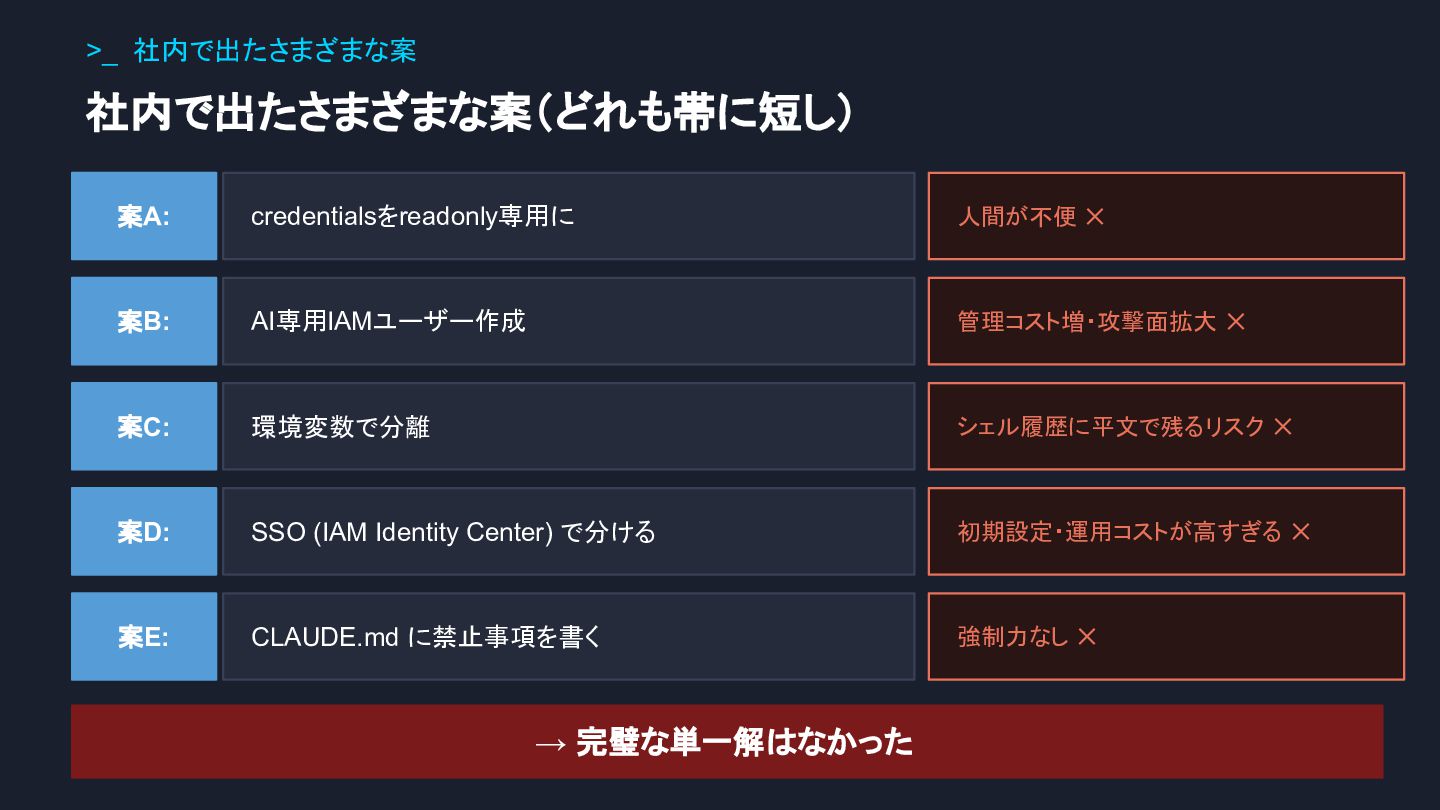
>_ 社内で出たさまざまな案 社内で出たさまざまな案(どれも帯に短し) 案A: credentialsをreadonly専用に 人間が不便 ✕ 案B: AI専用IAMユーザー作成 管理コスト増・攻撃面拡大
✕ 案C: 環境変数で分離 シェル履歴に平文で残るリスク ✕ 案D: SSO (IAM Identity Center) で分ける 初期設定・運用コストが高すぎる ✕ 案E: CLAUDE.md に禁止事項を書く 強制力なし ✕ → 完璧な単一解はなかった
> _ 現状の落としどころ:多層防御(第 1層) 1 { 2 "permissions": { 3
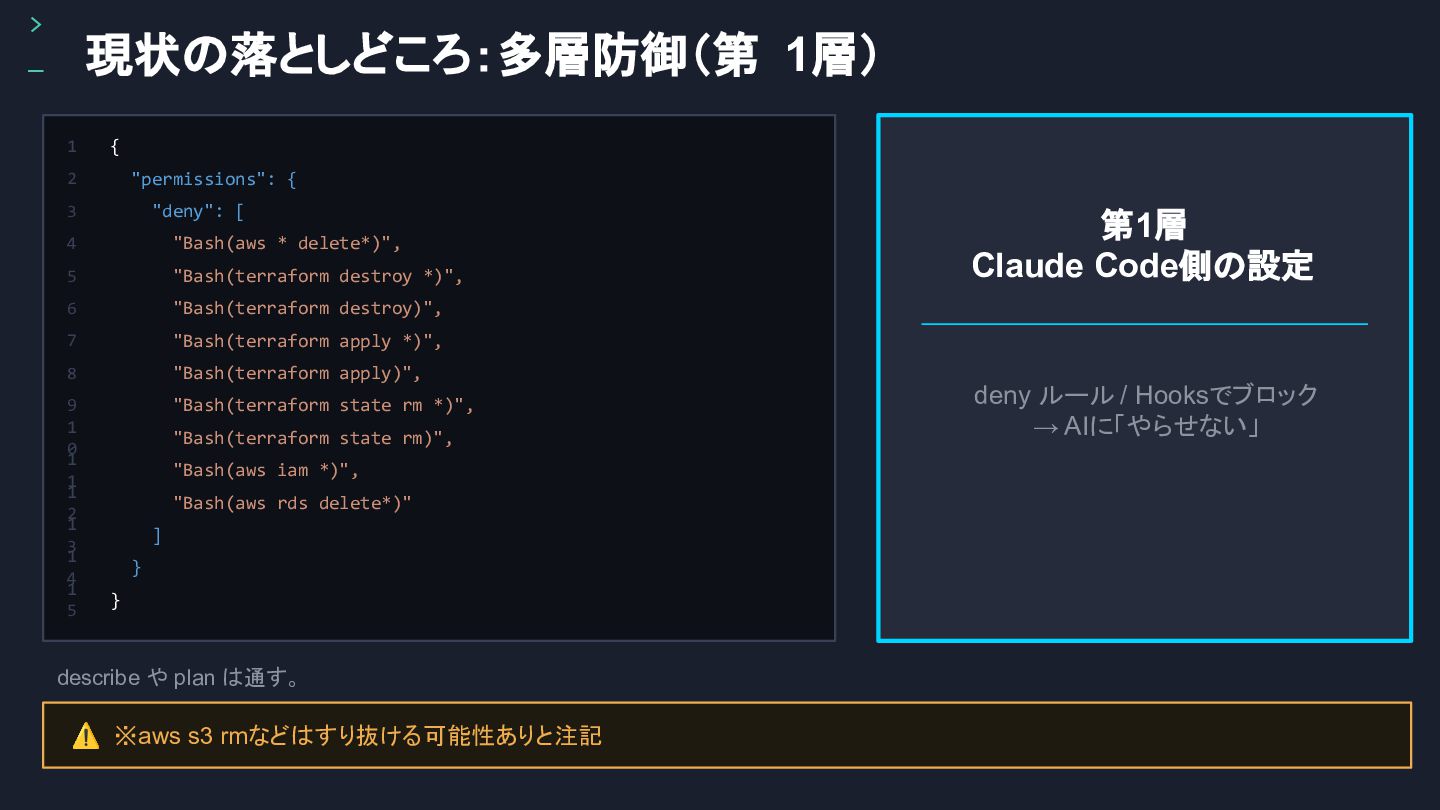
"deny": [ 4 "Bash(aws * delete*)", 5 "Bash(terraform destroy *)", 6 "Bash(terraform destroy)", 7 "Bash(terraform apply *)", 8 "Bash(terraform apply)", 9 "Bash(terraform state rm *)", 1 0 "Bash(terraform state rm)", 1 1 "Bash(aws iam *)", 1 2 "Bash(aws rds delete*)" 1 3 ] 1 4 } 1 5 } 第1層 Claude Code側の設定 deny ルール / Hooksでブロック → AIに「やらせない」 describe や plan は通す。 ⚠ ※aws s3 rmなどはすり抜ける可能性ありと注記
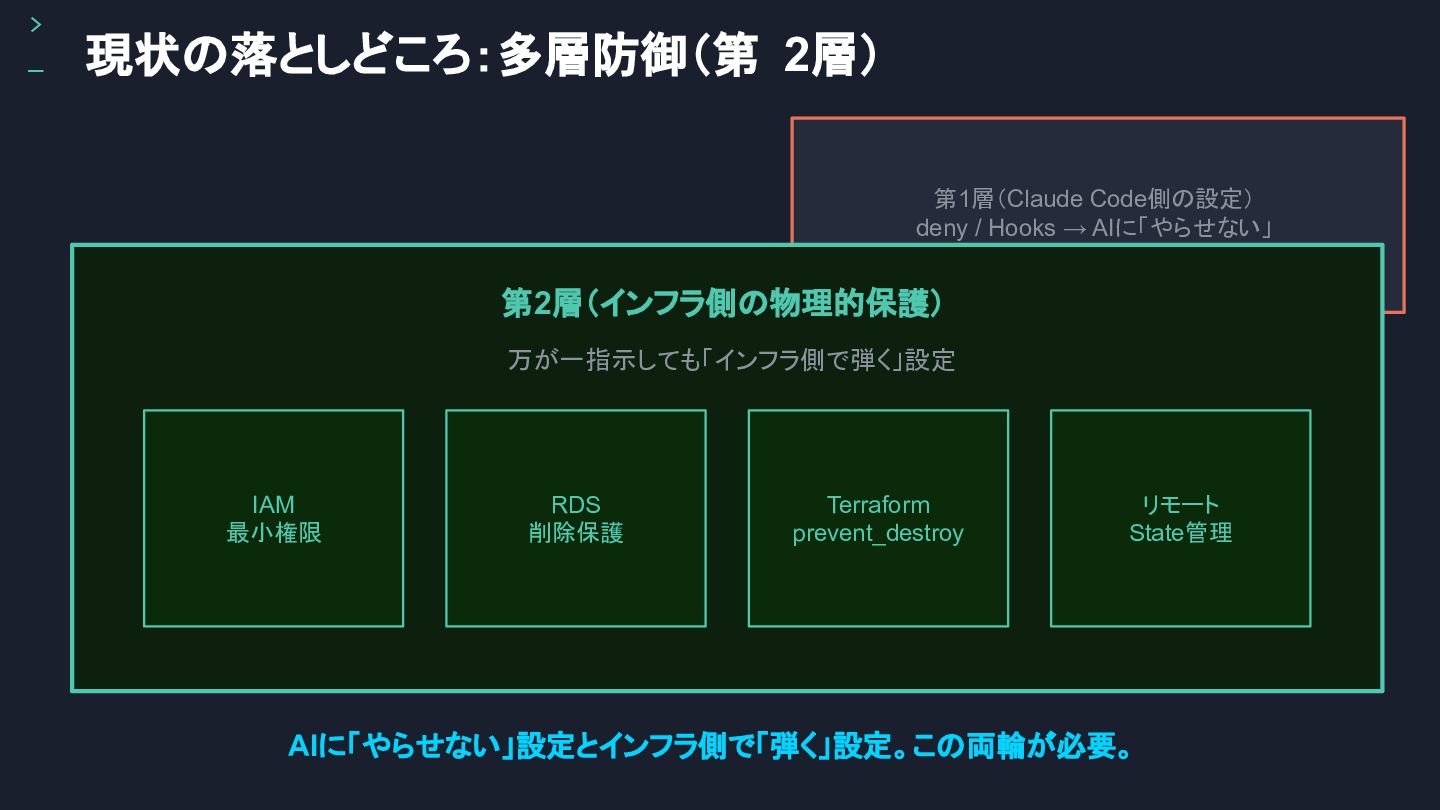
> _ 現状の落としどころ:多層防御(第 2層) 第1層(Claude Code側の設定) deny / Hooks →
AIに「やらせない」 第2層(インフラ側の物理的保護) 万が一指示しても「インフラ側で弾く」設定 IAM 最小権限 RDS 削除保護 Terraform prevent_destroy リモート State管理 AIに「やらせない」設定とインフラ側で「弾く」設定。この両輪が必要。
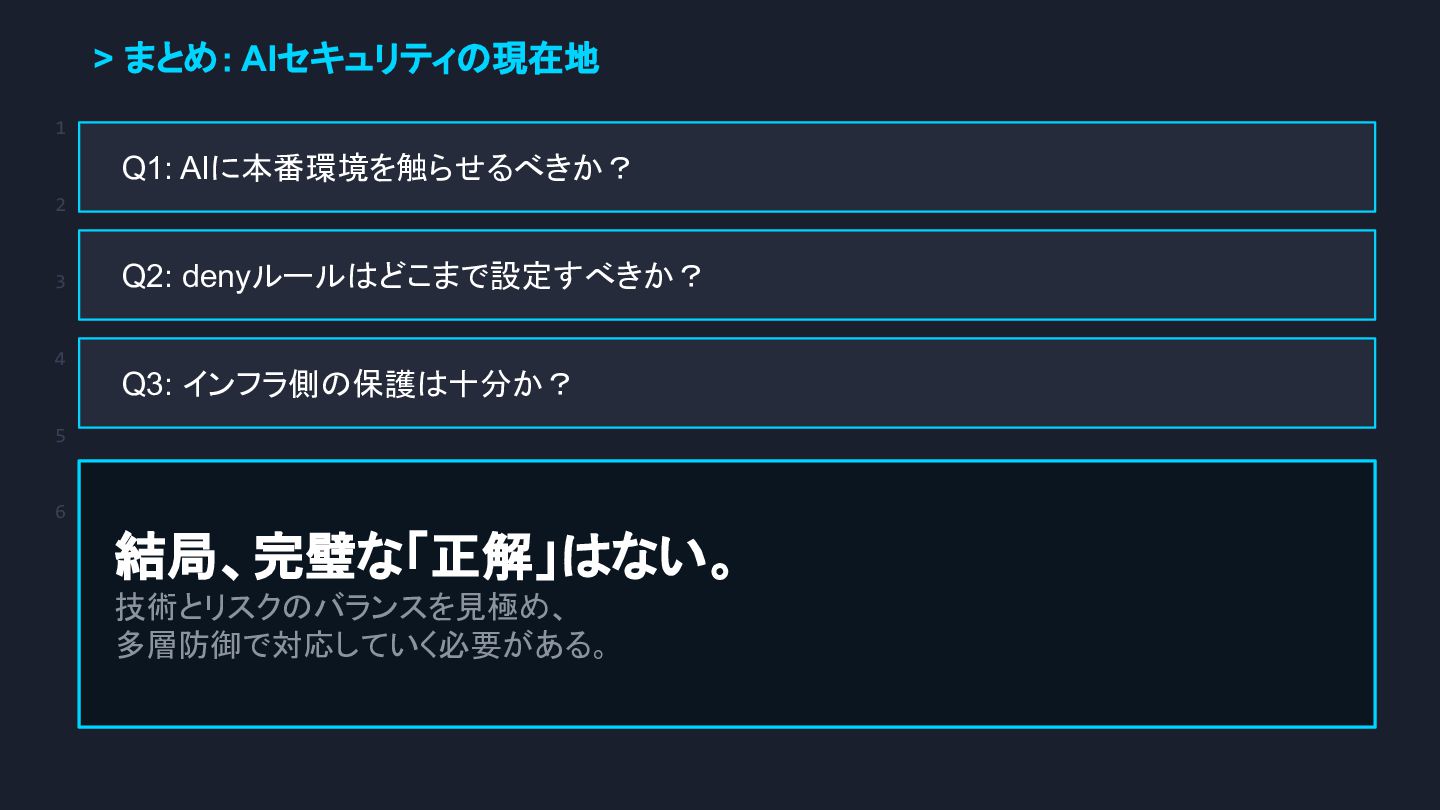
1 2 3 4 5 6 > まとめ:AIセキュリティの現在地 Q1: AIに本番環境を触らせるべきか?
Q2: denyルールはどこまで設定すべきか? Q3: インフラ側の保護は十分か? 結局、完璧な「正解」はない。 技術とリスクのバランスを見極め、 多層防御で対応していく必要がある。
1 2 3 4 5 6 7 8 9 10
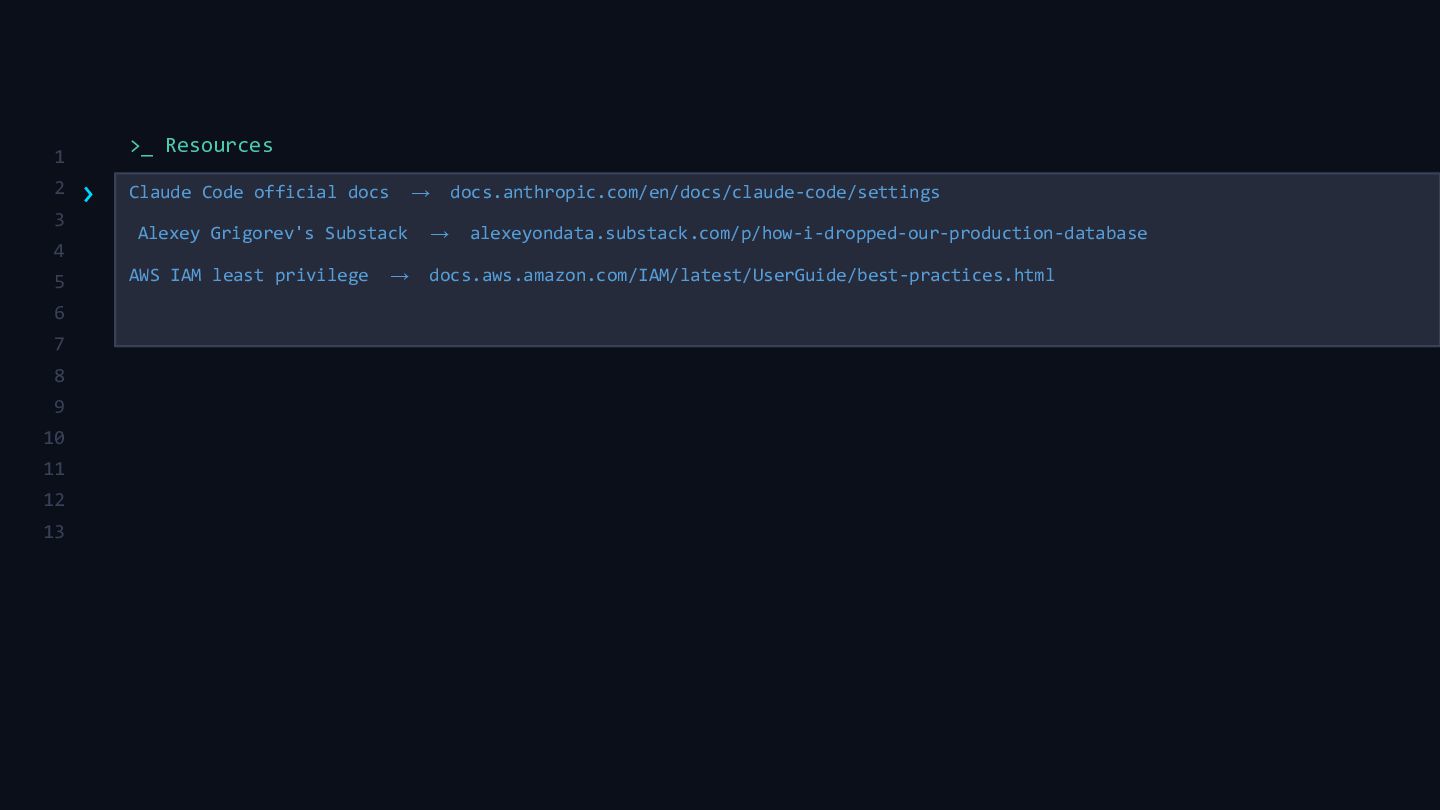
11 12 13 › >_ Resources Claude Code official docs → docs.anthropic.com/en/docs/claude-code/settings Alexey Grigorev's Substack → alexeyondata.substack.com/p/how-i-dropped-our-production-database AWS IAM least privilege → docs.aws.amazon.com/IAM/latest/UserGuide/best-practices.html


 shubox
 ktombow
 ivargrimstad
 raeminkang
 xleitix
 yasunori0418
 yuta_onishi_97
 steliosf
 mitohato14
 sobolevn
 quramy
 skryukov
 kasacchiful
 axbom
 helenjbeal
 tomoyanonymous
 codingconduct
 dougneiner
 tamaranovitovic
 kneath
 apolaine
 honnibal
 jonoalderson
 marktimemedia