Upgrade to Pro — share decks privately, control downloads, hide ads and more …

A Basic Guide to Advanced Incident Response: Ar...

Sponsored · Ship Features Fearlessly Turn features on and off without deploys. Used by thousands of Ruby developers. →
Scott J. Roberts
September 06, 2014

A Basic Guide to Advanced Incident Response: ArchCon Edition

Presented at the first (and insanely awesome) ArchCon 2014 in St Louis Mo.

Scott J. Roberts

September 06, 2014

Transcript

90 slides
  1. What I do all Day - Identify and respond to

    Security Incidents - Collaborate with 3rd parties to respond to their incidents - Build tools to assist those above
  2. I should warn you: ! I always wanted to be

    a Spy I blame watching too much James Bond as a kid…
  3. Indicators - IP addresses - URLs & Domains - Malware

    - Hashes (Absolute & Fuzzy) - Capabilities (What it does, how it talks) - Certificates, Email addresses, User Agent Strings, etc
  4. Wikis for Great Justice - Wikis are great for dynamically

    structured data - Makes collaboration Easy - I’ve shared threat intel and incident templates (Linked at the End) - The Price is right…
  5. Online Services Malicious IP Lists IPVoid, URLVoid, & MyWOT URLQuery

    & Wepawet Virus Total & Malwr Shodan CentralOps, Robtext, & Ip2location
  6. Vendor Info - Vendor Blogs, Reports & podcasts Often have

    piles of data and indicators - Verizon’s Data Breach Investigations report is a yearly favorite - Look for resources from companies like Mandiant/FiReEye, Dell SecureWorks, AlienVault, and Crowdstrike Just watch out… they’re trying to sell you something…
  7. “Gathering Intel from others gives you a view of their

    world. Gather your own raw data and generate Intel to view and learn about yours.” - @mJxG
  8. Developing Your Own Intel - Think about What is important

    to determine who might attack and then decide how it could happen - Go “hunting” - Listen to your Users - Review & Iterate on your Own Incidents
  9. “What's everyone's fascination with actionable intelligence? Your C-suite wants colorful

    charts and projects with cool acronyms.” - @infosecjerk
  10. geographic Location Parent Organization including unit names Individual Actor names,

    ranks, pictures, & Physical addresses Interesting Only Academically
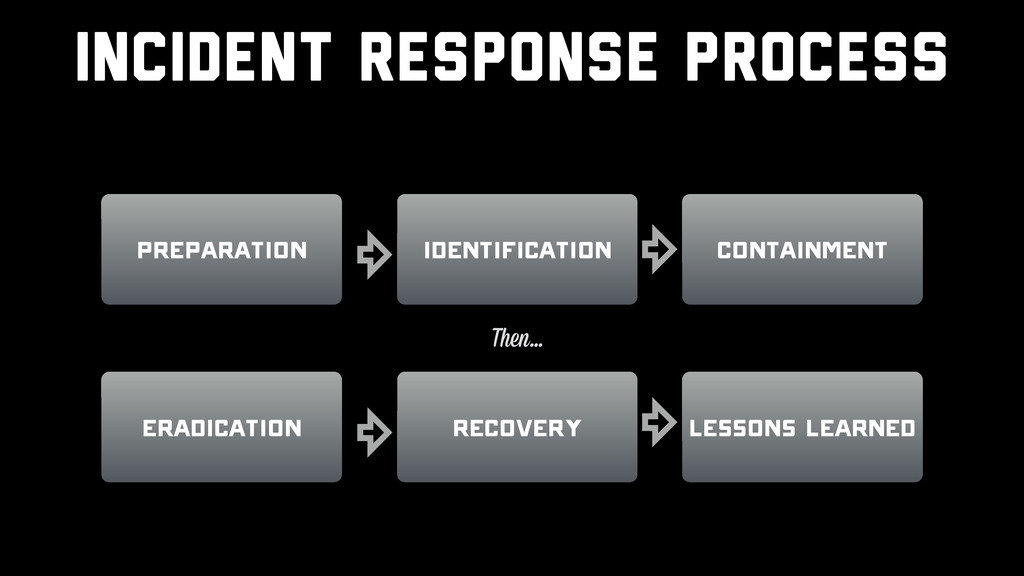
  11. “If your incident response methodology doesn't let you deviate from

    the methodology, you're doing it wrong. Agility is key.” - @smoothimpact
  12. Every Incident Response Starts a Vulnerability Assessment Every Vulnerability Assessment

    Starts An Incident Response For one iteration… most of the time…
  13. Every Incident Response Starts a Vulnerability Assessment Every Vulnerability Assessment

    Starts An Incident Response For one iteration… most of the time…
  14. - MIG is OpSec's platform for investigative surgery of remote

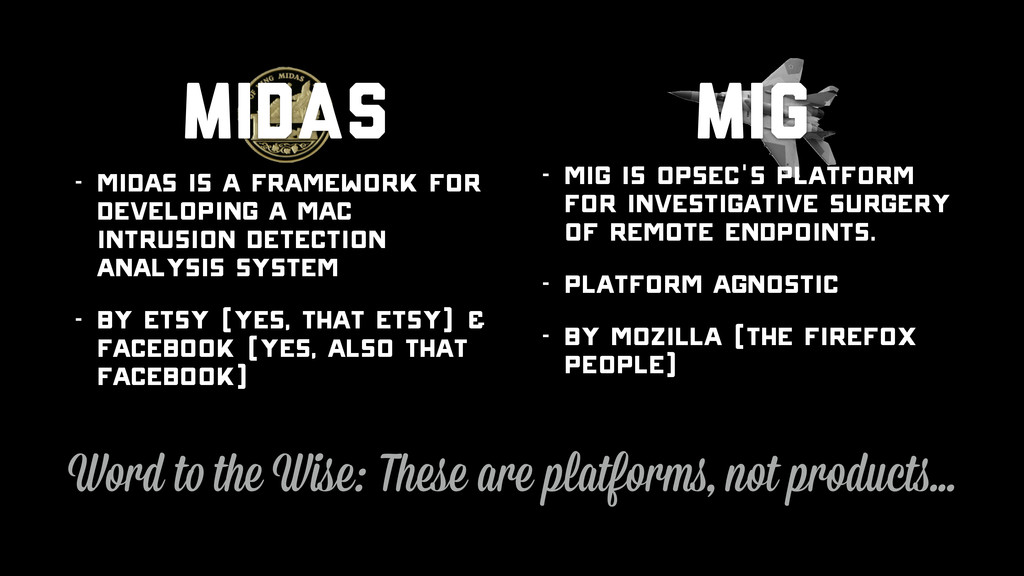
    endpoints. - Platform Agnostic - By Mozilla (The Firefox people) - MIDAS is a framework for developing a Mac Intrusion Detection Analysis System - By Etsy (yes, that Etsy) & Facebook (Yes, also that Facebook) Mig Word to the Wise: These are platforms, not products… MIDAS
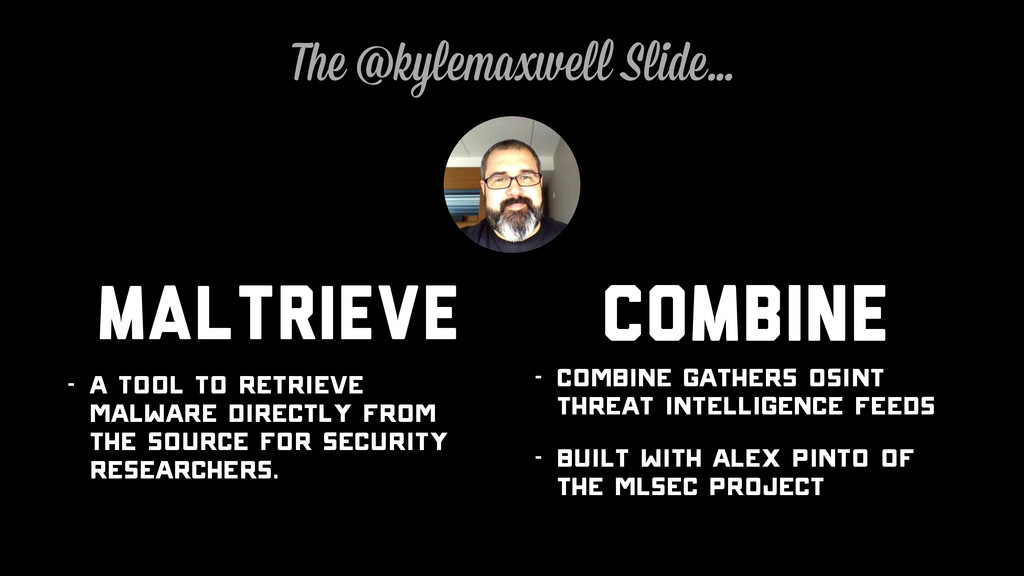
  15. - Combine gathers OSINT Threat Intelligence Feeds - Built with

    Alex Pinto of the MLSec Project - A tool to retrieve malware directly from the source for security researchers. The @kylemaxwell Slide… Maltrieve Combine
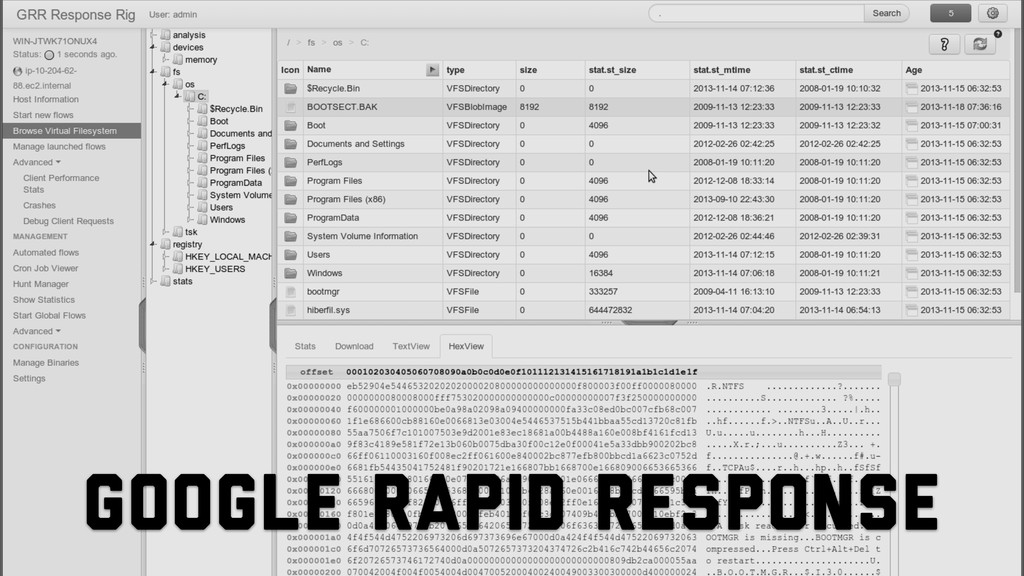
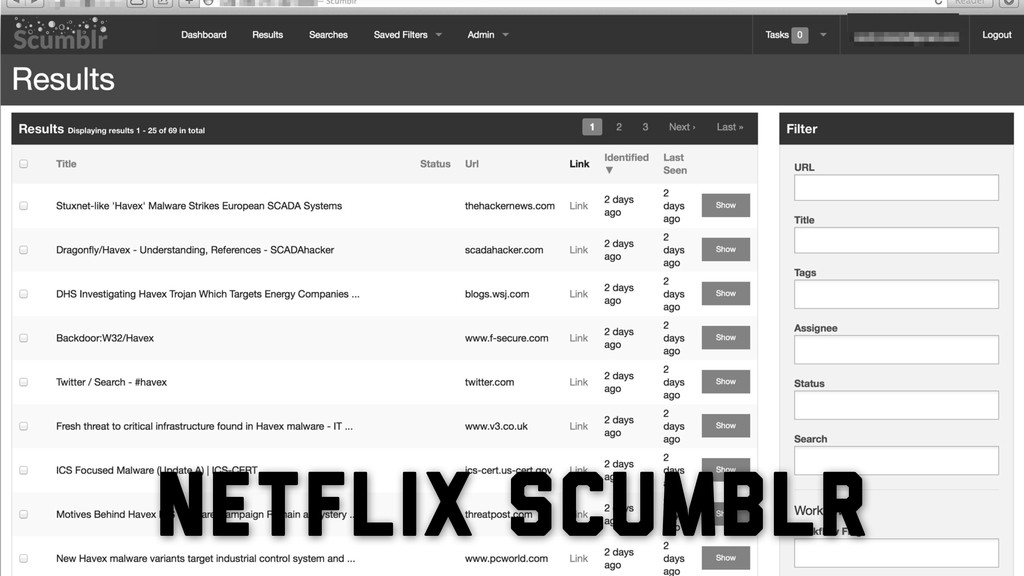
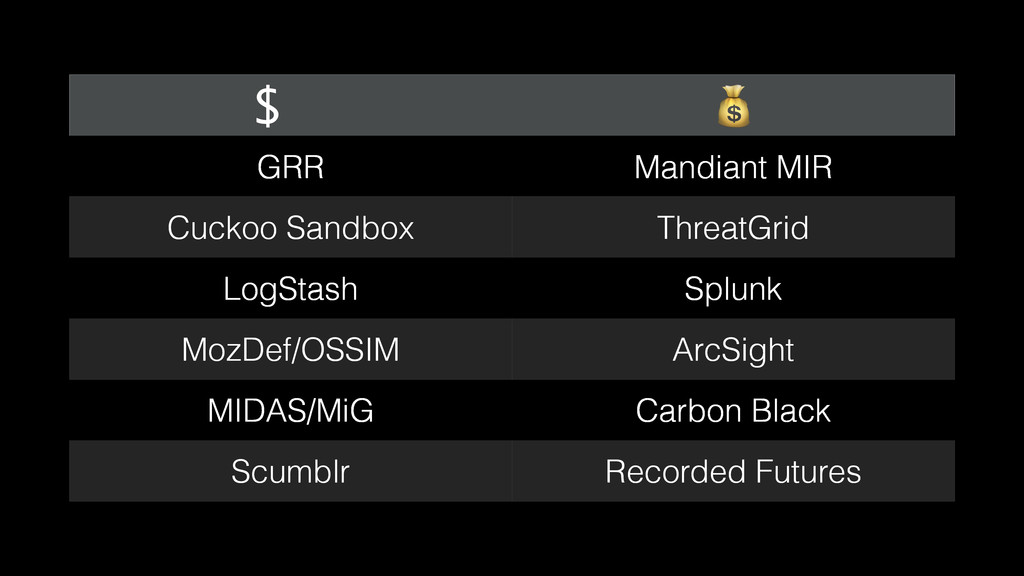
  16. $0 GRR Mandiant MIR Cuckoo Sandbox ThreatGrid LogStash Splunk MozDef/OSSIM

    ArcSight MIDAS/MiG Carbon Black Scumblr Recorded Futures
  17. cat *.json | jq '.[] | if .action == "user.login"

    then "\(.actor_ip), \ (.actor)" else "" end' | sort | uniq | sed -e 's/"//g' > userlogin-ip-to-user.csv
  18. python, ruby, etc - Log Parsing and Manipulation - Automating

    tasks - Modifying and Extending tools - Building tools that simply don’t exist
  19. […] God forbid DFIRs learned a programming language, they might

    start writing automated tools. - @postmodern_mod3
  20. Conclusion… -Intelligence Driven Incident Response is the new Normal -Open

    Source is making $$$ less important than Intel -Collaboration is Key

More Decks by Scott J. Roberts

Other Decks in Technology