Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
ハニーポットから見たWebサーバへの攻撃
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
taiko19xx
December 15, 2018
Technology
3k
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
ハニーポットから見たWebサーバへの攻撃
taiko19xx
December 15, 2018
More Decks by taiko19xx
See All by taiko19xx
Bedrockで遊ぼう! 短期間で色々開発してみた
taiko19xx
1
200
Incident Managerでインシデント発生時のエスカレーションを自動化する
taiko19xx
0
290
Lambdaカスタムランタイムで PHPでもサーバーレス!
taiko19xx
0
100
IoTっぽいアプリをk3s+Raspberry Piで実行する
taiko19xx
0
370
PHPなプロダクトをAmazon ECSで開発運用してる話
taiko19xx
0
1.4k
RaspberryPi+AWSでIoT(っぽ い)GPSロガーを作ってみた
taiko19xx
0
1.7k
PHPからWin32APIをいじってみた
taiko19xx
0
1.8k
Other Decks in Technology
See All in Technology
渡米前の準備を制す!re:Invent 2026徹底準備術 / The Ultimate Preparation Guide for re:Invent 2026
yuj1osm
1
480
AI時代のエンジニアの情報発信〜個人の発信を組織の力に変える〜
ryo_kawamata
0
6.5k
バイブコーディングの特徴と「コケて直す」ループ
happysamurai294
0
140
複雑な業務システムを高速でつくるため、チーム全員をつくれる人へ
ayakurabuchi
0
120
【Oracle AI SPOTLIGHT ウェビナー】事例から見る!なぜOCIが選ばれたのか ― AI時代のクラウド戦略を紐解く ―
oracle4engineer
PRO
1
150
Lint の層を組み直した話
bengo4com
1
280
あなたのDartコードは丸見えかもしれない ~reFlutterで暴くFlutterアプリの中身と多層防御~
zozotech
PRO
0
730
Don't write the architecture only in the prompt.
neohsu
0
290
reInvent2026stby LT00 "Change your life!"
shinichirokawano
1
520
Oracle Database Security 詳細解説
oracle4engineer
PRO
1
190
視野はAIに、視座は人に / ai-for-breadth-humans-for-perspective
nkzn
6
2.7k
新卒エンジニア、 介護士になる
ryu1013
1
660
Featured
See All Featured
Side Projects
sachag
456
43k
30 Presentation Tips
portentint
PRO
1
450
Unsuck your backbone
ammeep
672
58k
Leading Effective Engineering Teams in the AI Era
addyosmani
9
2.8k
Responsive Adventures: Dirty Tricks From The Dark Corners of Front-End
smashingmag
254
23k
It's Worth the Effort
3n
188
29k
Joys of Absence: A Defence of Solitary Play
codingconduct
1
570
Typedesign – Prime Four
hannesfritz
42
3.2k
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
Introduction to Domain-Driven Design and Collaborative software design
baasie
1
1.1k
Documentation Writing (for coders)
carmenintech
77
5.6k
XXLCSS - How to scale CSS and keep your sanity
sugarenia
250
1.3M
Transcript
ハニーポットから見た Webサーバへの攻撃 PHP Conference 2018 Lightning Talk@2018/12/15 @taiko19xx / 木村
俊彦
こんにちは!
突然ですが ハニーポット知ってる人?
では、 ハニーポット植えてる人?
今回の話 • 趣味で植えてるハニーポットで記録したログにどんな 攻撃があったか?という話です • 2018年4月~12月までのデータを集計した結果です • 環境によって差異があるのであくまで参考程度に • 最近いろいろあるので具体的な攻撃手法についてはあ
まり触れません • あしからず
PHPに関係した?ログ
PHP関係で 一番多かったのは 何でしょう?
None
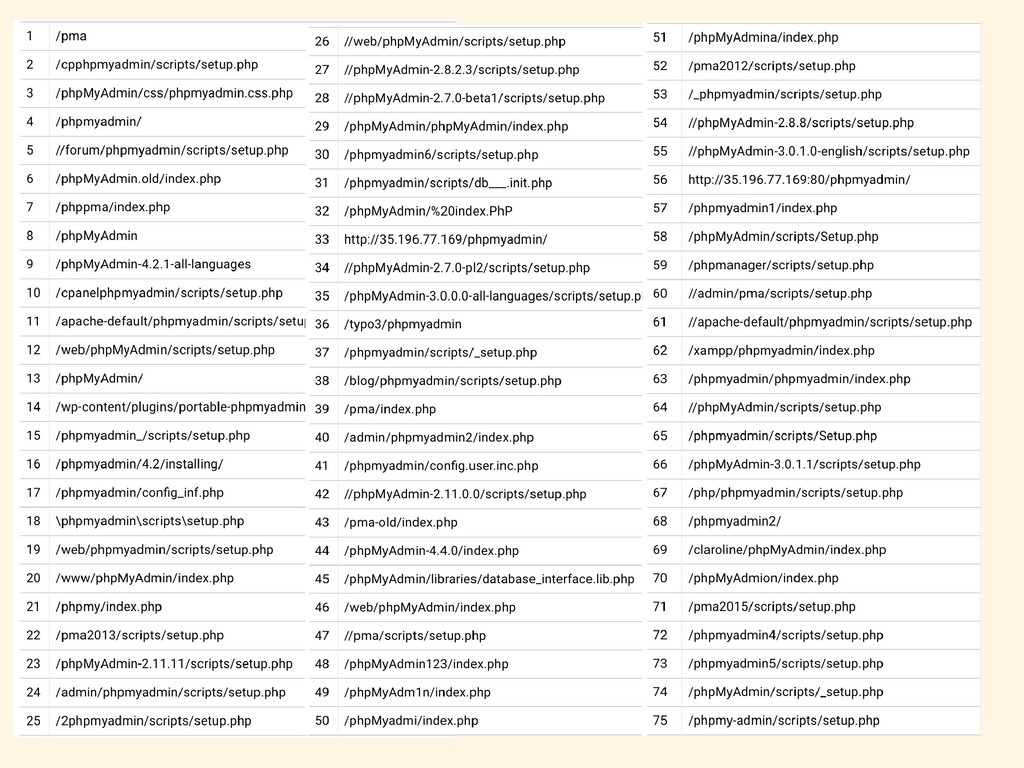
phpMyAdmin • とにかく多い • 件数というよりはパターンが多い • 攻撃よりは存在チェックがメイン • あらゆるディレクトリに名変えて試行錯誤してくる
None
None
None
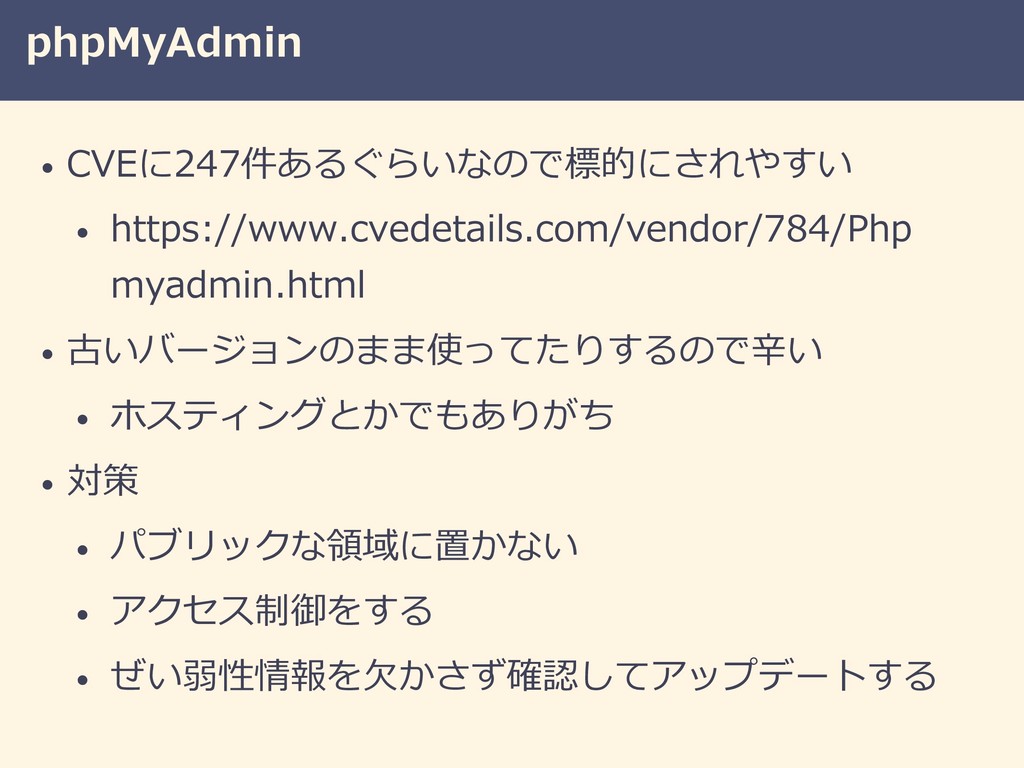
phpMyAdmin • CVEに247件あるぐらいなので標的にされやすい • https://www.cvedetails.com/vendor/784/Php myadmin.html • 古いバージョンのまま使ってたりするので辛い • ホスティングとかでもありがち
• 対策 • パブリックな領域に置かない • アクセス制御をする • ぜい弱性情報を欠かさず確認してアップデートする
CMSでは?
None
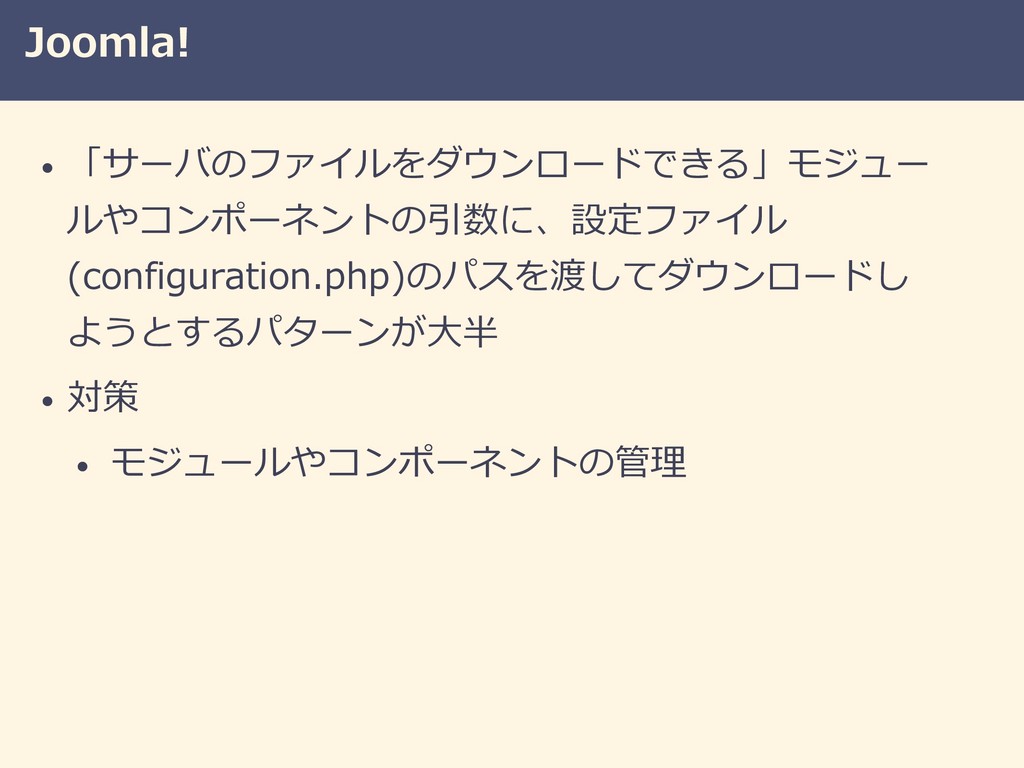
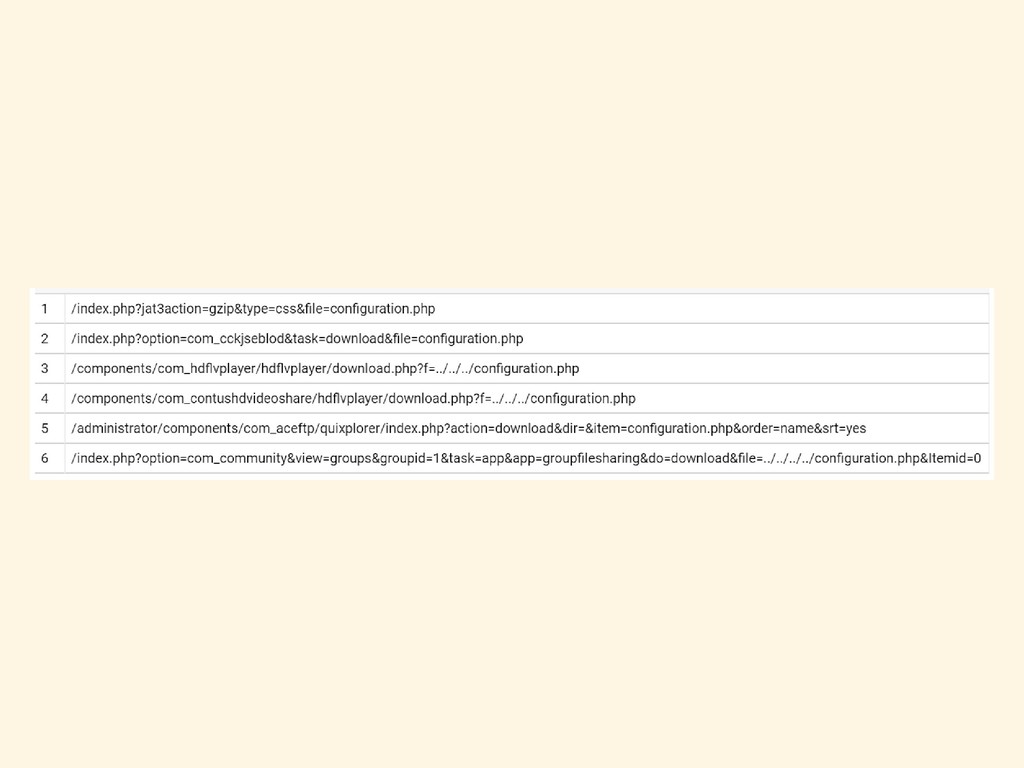
Joomla! • 「サーバのファイルをダウンロードできる」モジュー ルやコンポーネントの引数に、設定ファイル (configuration.php)のパスを渡してダウンロードし ようとするパターンが大半 • 対策 • モジュールやコンポーネントの管理
None
WordPress • ログイン画面への辞書攻撃 • wp-login.php • 設定ファイルを直で取得しようとしてくる • wp-config.php •
対策 • 安易なユーザーとパスワードはやめましょう • .htaccessなどでwp-config.phpを保護
Drupal • Drupalgeddon 2の攻撃が何件か • CVE-2018-7600 • https://www.jpcert.or.jp/at/2018/at180012.ht ml •
名前はかっこいい • 対策 • 対策済みのバージョンにアップデートする • Drupal 8.5.1/7.58/8.4.6/8.3.9 以上 • 8.2以前や6系にはパッチなしなので注意
その他
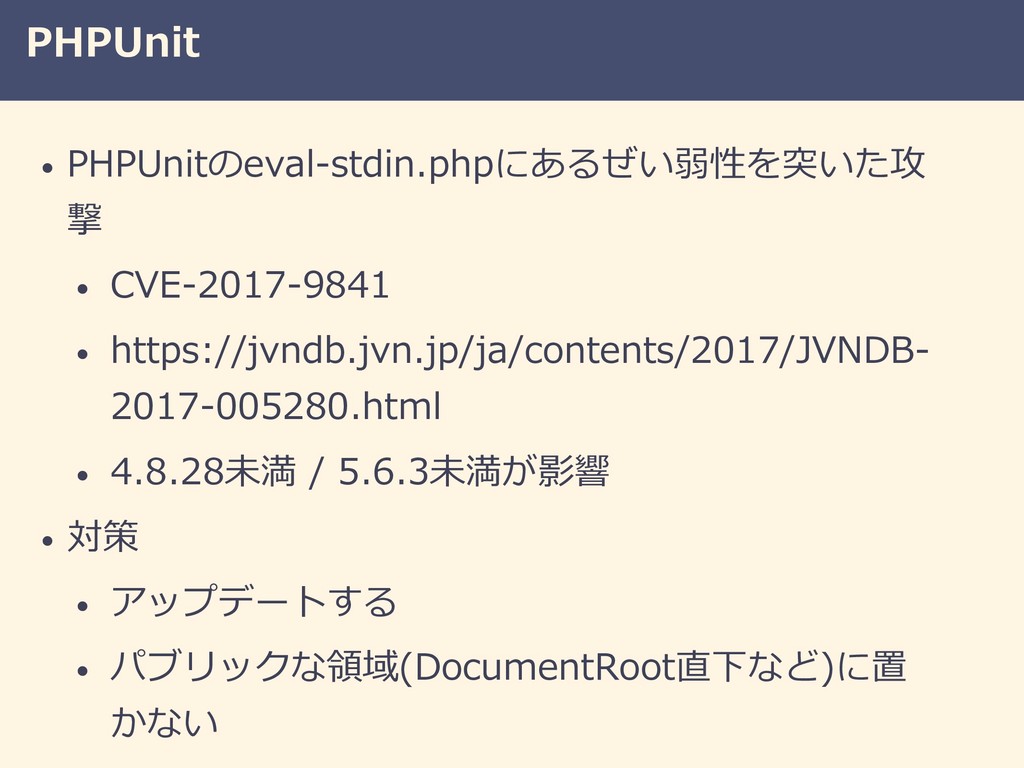
PHPUnit • PHPUnitのeval-stdin.phpにあるぜい弱性を突いた攻 撃 • CVE-2017-9841 • https://jvndb.jvn.jp/ja/contents/2017/JVNDB- 2017-005280.html •
4.8.28未満 / 5.6.3未満が影響 • 対策 • アップデートする • パブリックな領域(DocumentRoot直下など)に置 かない
None
PHP関係ない?ログ
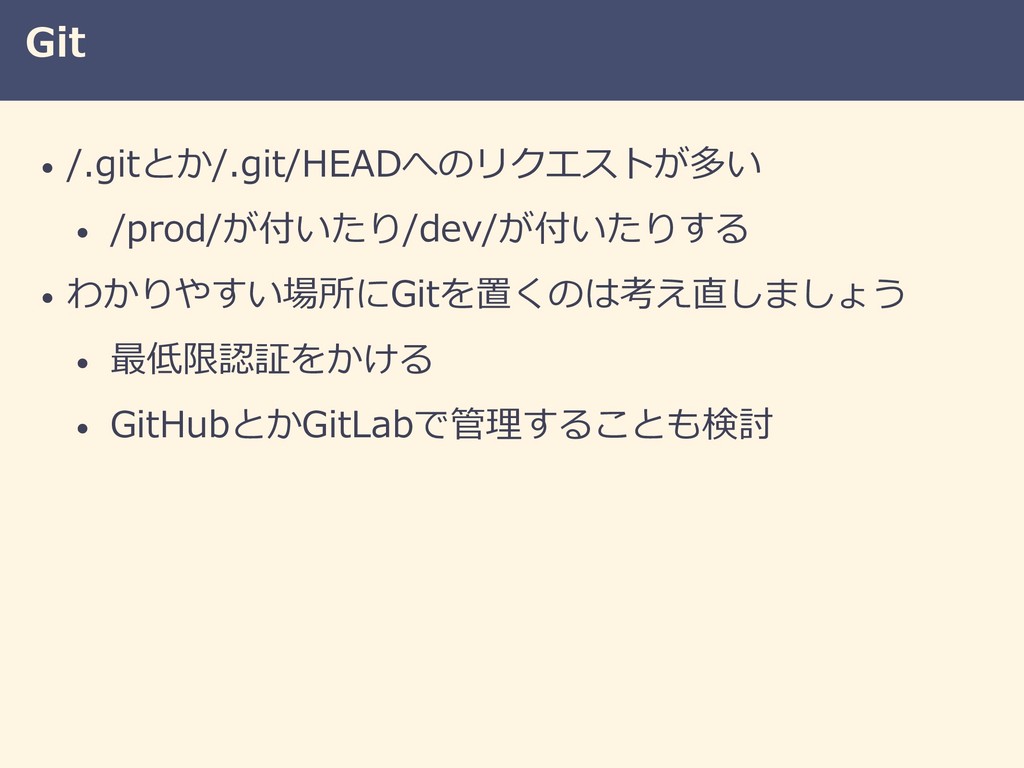
Git • /.gitとか/.git/HEADへのリクエストが多い • /prod/が付いたり/dev/が付いたりする • わかりやすい場所にGitを置くのは考え直しましょう • 最低限認証をかける •
GitHubとかGitLabで管理することも検討
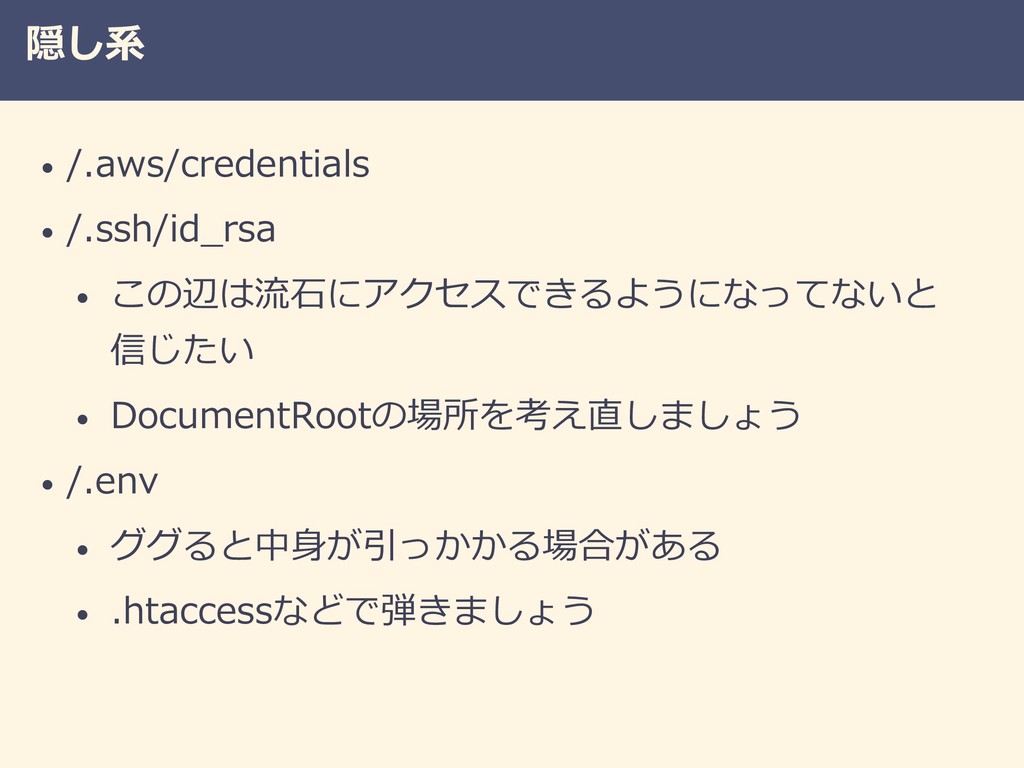
隠し系 • /.aws/credentials • /.ssh/id_rsa • この辺は流石にアクセスできるようになってないと 信じたい • DocumentRootの場所を考え直しましょう
• /.env • ググると中身が引っかかる場合がある • .htaccessなどで弾きましょう
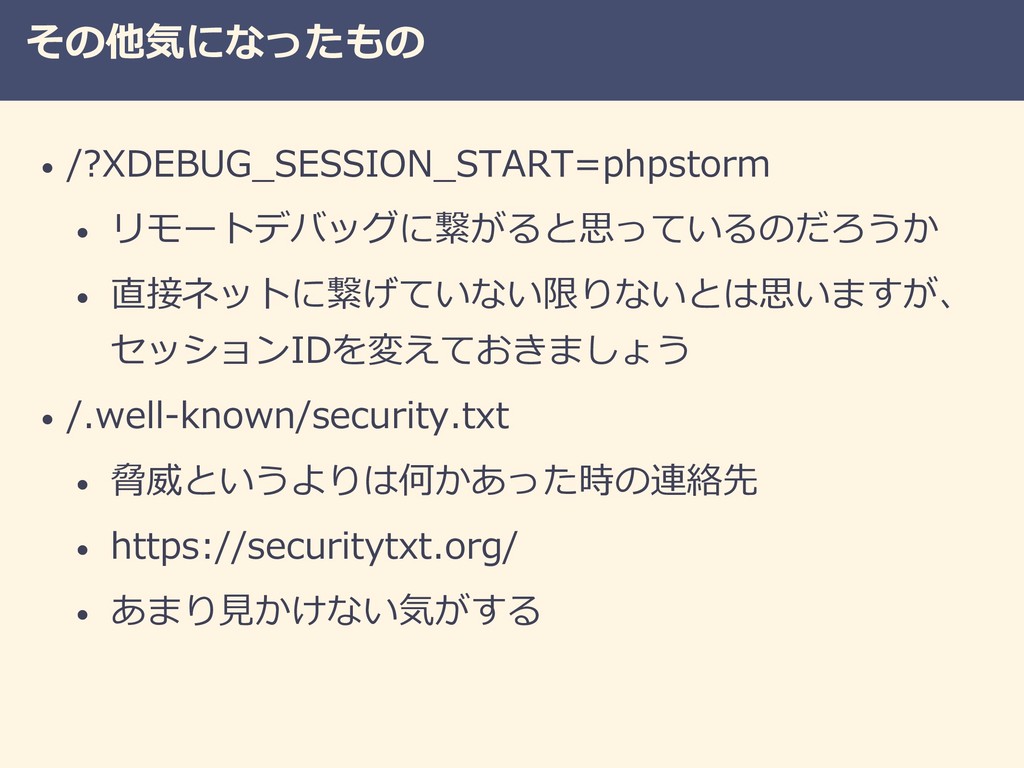
その他気になったもの • /?XDEBUG_SESSION_START=phpstorm • リモートデバッグに繋がると思っているのだろうか • 直接ネットに繋げていない限りないとは思いますが、 セッションIDを変えておきましょう • /.well-known/security.txt
• 脅威というよりは何かあった時の連絡先 • https://securitytxt.org/ • あまり見かけない気がする
最後に • 紹介できなかったものは沢山あります • 「/manager/html」が4万件越えのリクエストが あるとか • 時期によって流行廃りがあるとか • こういうのが見られるのでハニーポットは楽しい
• 植える際はセキュリティに気を付ける • ミイラ取りがミイラになってしまうので…
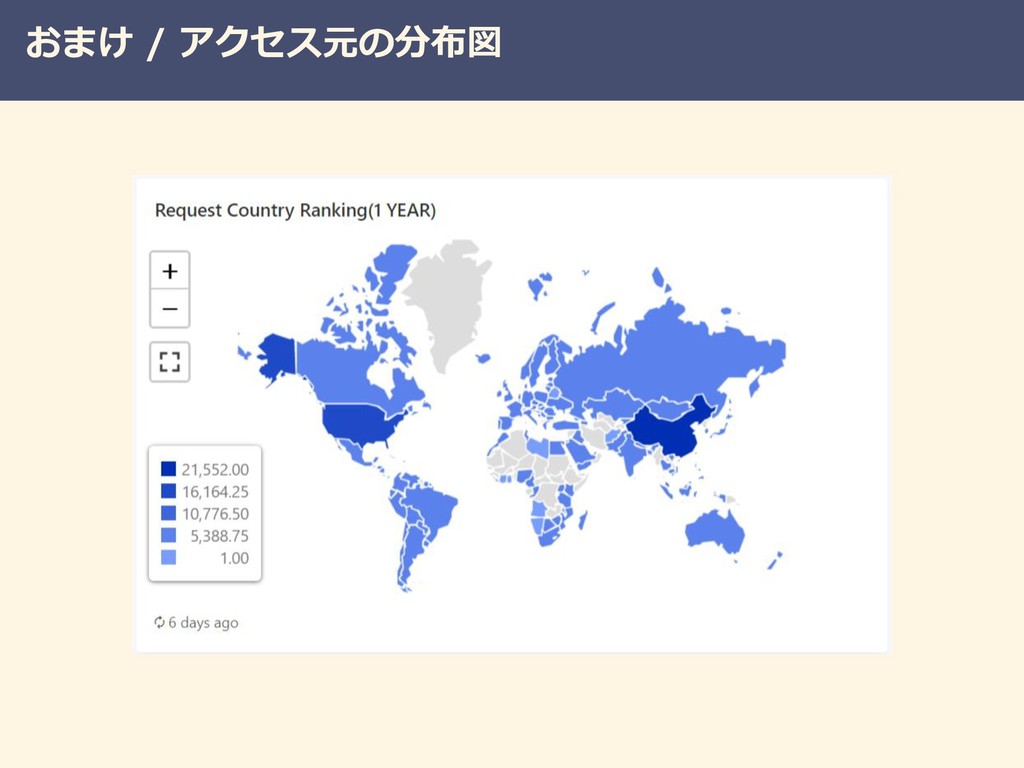
おまけ / アクセス元の分布図
自己紹介 • 木村俊彦(@taiko19xx) • 普段はAzure/AWSを構築したりいじったり • もちろんPHPも • 仙台から来ました
仙台といえば
None
チケット販売中! 本編 懇親会


 taiko19xx
 yuj1osm
 ryo_kawamata
 happysamurai294
 ayakurabuchi
 oracle4engineer
 bengo4com
 zozotech
 neohsu
 shinichirokawano
 nkzn
 ryu1013
 sachag
 portentint
 ammeep
 addyosmani
 smashingmag
 3n
 codingconduct
 hannesfritz
 eileencodes
 baasie
 carmenintech
 sugarenia