Share
Embed
How to Find Bugs in CosmWasm Smart Contract?
Doyeon Kim (LINE Plus / Security R&D / Security Researcher)
https://tech-verse.me/ja/sessions/88
https://tech-verse.me/en/sessions/88
https://tech-verse.me/ko/sessions/88
Tech-Verse2022
November 18, 2022
Transcript
63 slides
-
Who am I? › Experience › Security Research Engineer, LINE
› Main Works › Security Research › Security Consulting › Research Interests › Computer Software Security › Fuzz Testing › Smart Contract Security -
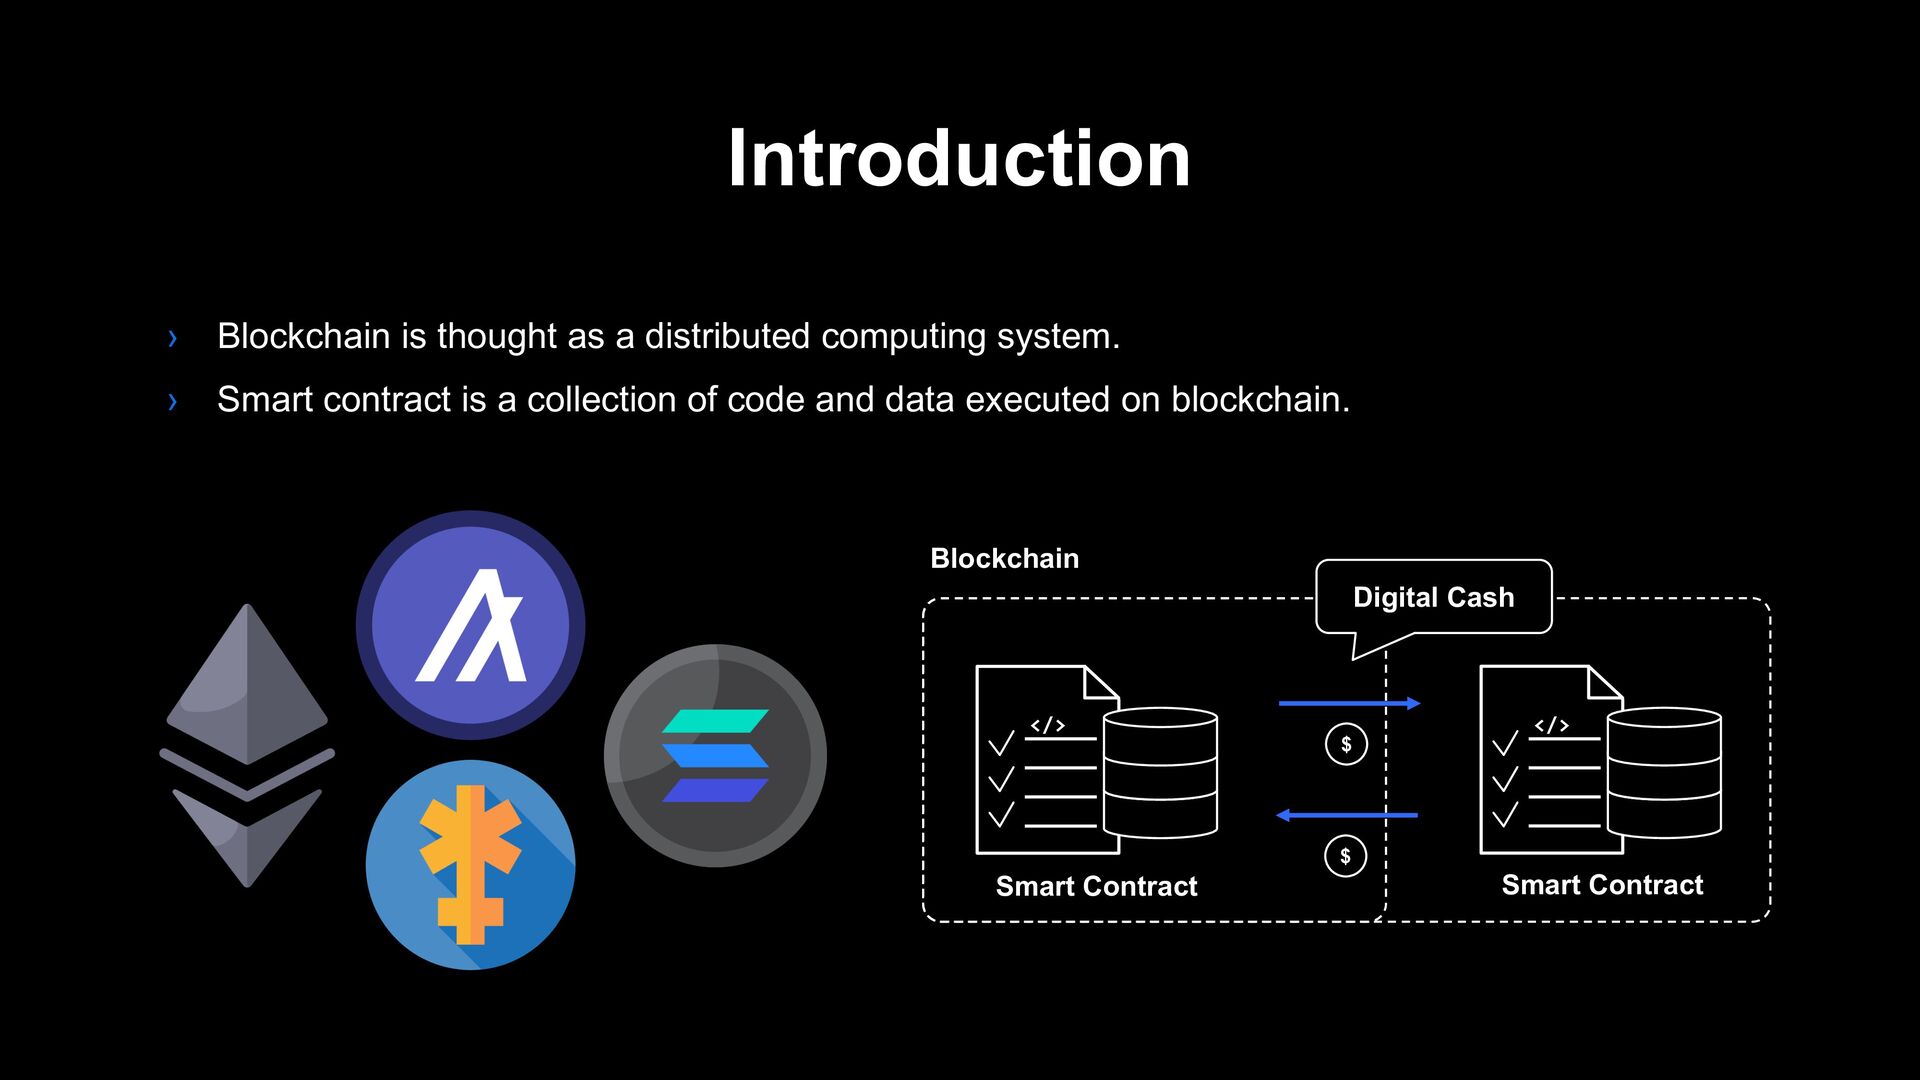
Introduction › Blockchain is thought as a distributed computing system.
› Smart contract is a collection of code and data executed on blockchain. $ Blockchain $ </> Digital Cash </> Smart Contract Smart Contract -
Introduction › There are several blockchain businesses in LINE. ›
Examples: BITFRONT, LINE BITMAX, LINK, LINE NFT … -
Introduction › There are several blockchain businesses in LINE. ›
Examples: BITFRONT, LINE BITMAX, LINK, LINE NFT … › LINE uses CosmWasm smart contract written in Rust. -
Introduction › There are several blockchain businesses in LINE. ›
Examples: BITFRONT, LINE BITMAX, LINK, LINE NFT … › LINE uses CosmWasm smart contract written in Rust. › CosmWasm is a smart contracting platform built for the Cosmos ecosystem[1]. › Cosmos is an ecosystem of blockchains that can scale and interoperate with each other[2]. [1] https://docs.cosmwasm.com/docs/1.0/ [2] https://v1.cosmos.network/intro -
Introduction › There are several blockchain businesses in LINE. ›
Examples: BITFRONT, LINE BITMAX, LINK, LINE NFT … › LINE uses CosmWasm smart contract written in Rust. › CosmWasm is a smart contracting platform built for the Cosmos ecosystem[1]. › Cosmos is an ecosystem of blockchains that can scale and interoperate with each other[2]. › CosmWasm smart contract runs the WebAssembly virtual machine. cf. Ethereum smart contract [1] https://docs.cosmwasm.com/docs/1.0/ [2] https://v1.cosmos.network/intro -
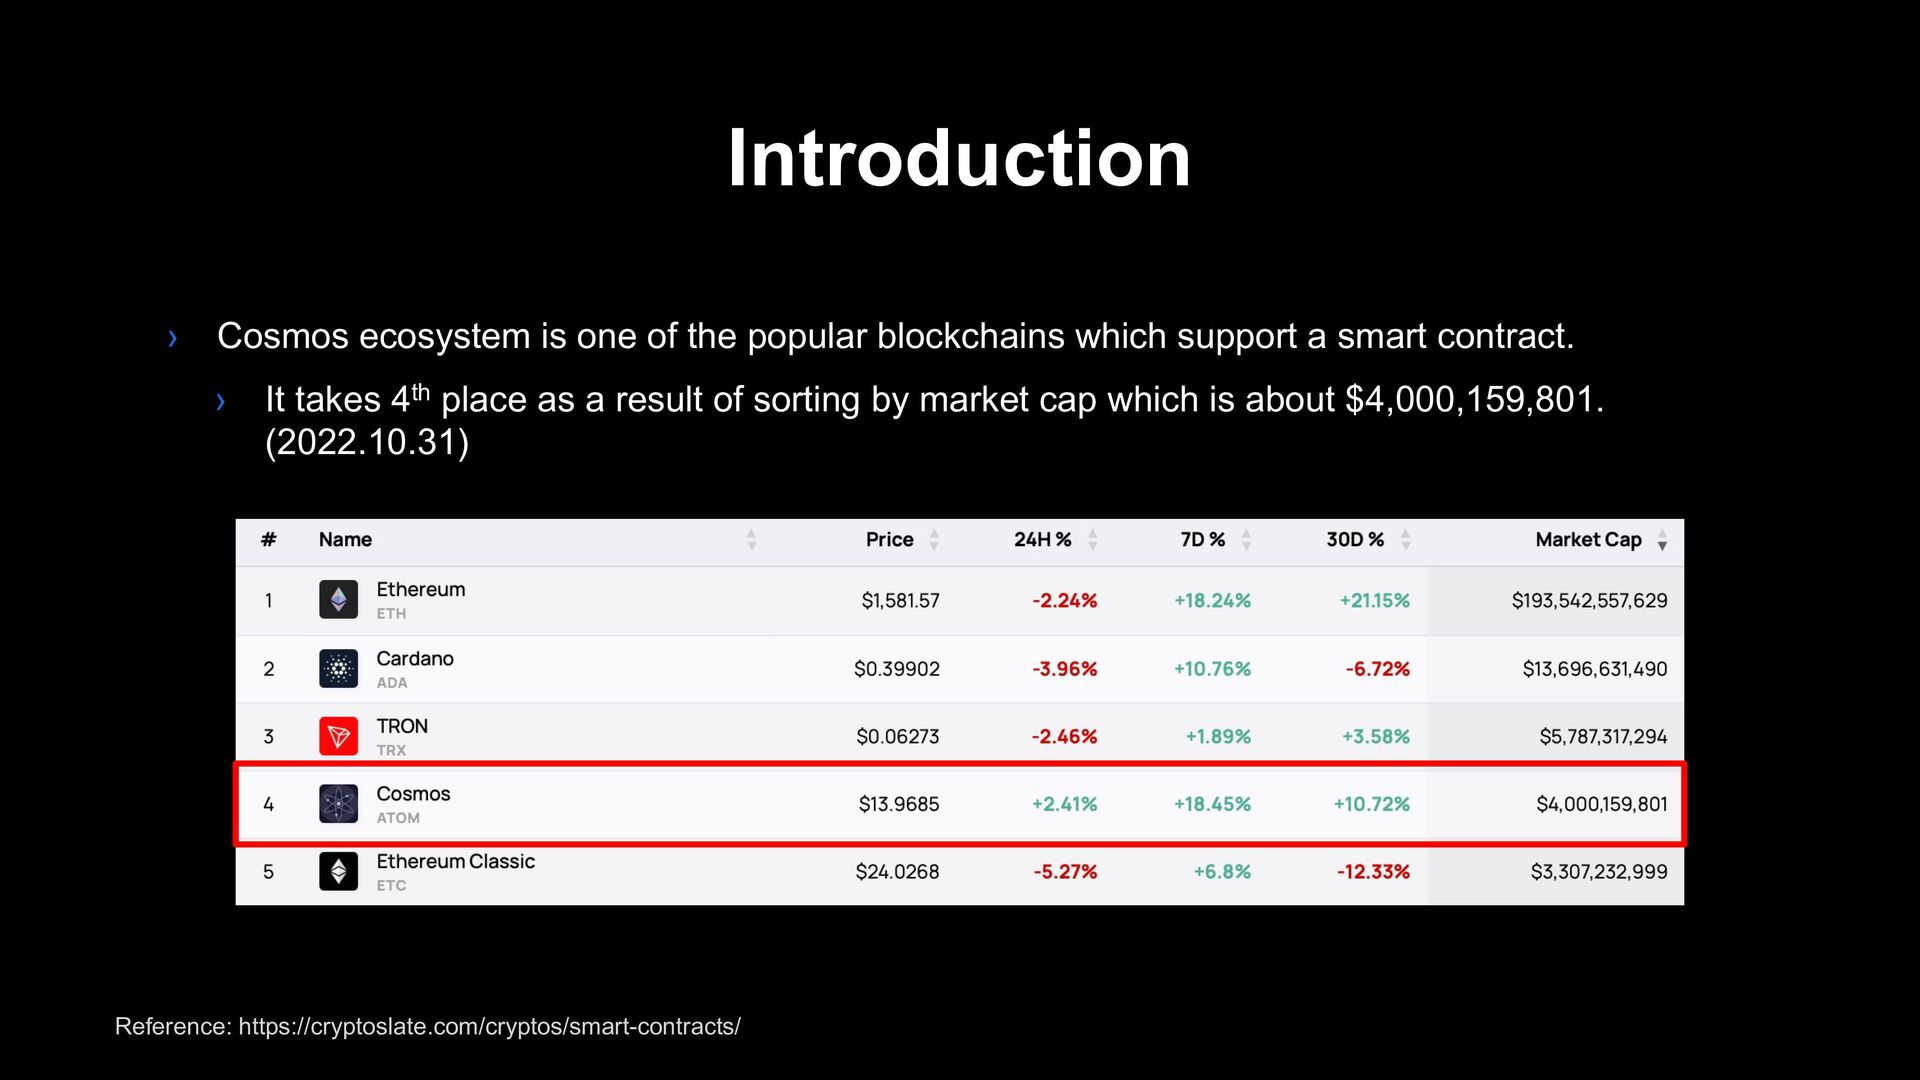
Introduction › Cosmos ecosystem is one of the popular blockchains
which support a smart contract. › It takes 4th place as a result of sorting by market cap which is about $4,000,159,801. (2022.10.31) Reference: https://cryptoslate.com/cryptos/smart-contracts/ -
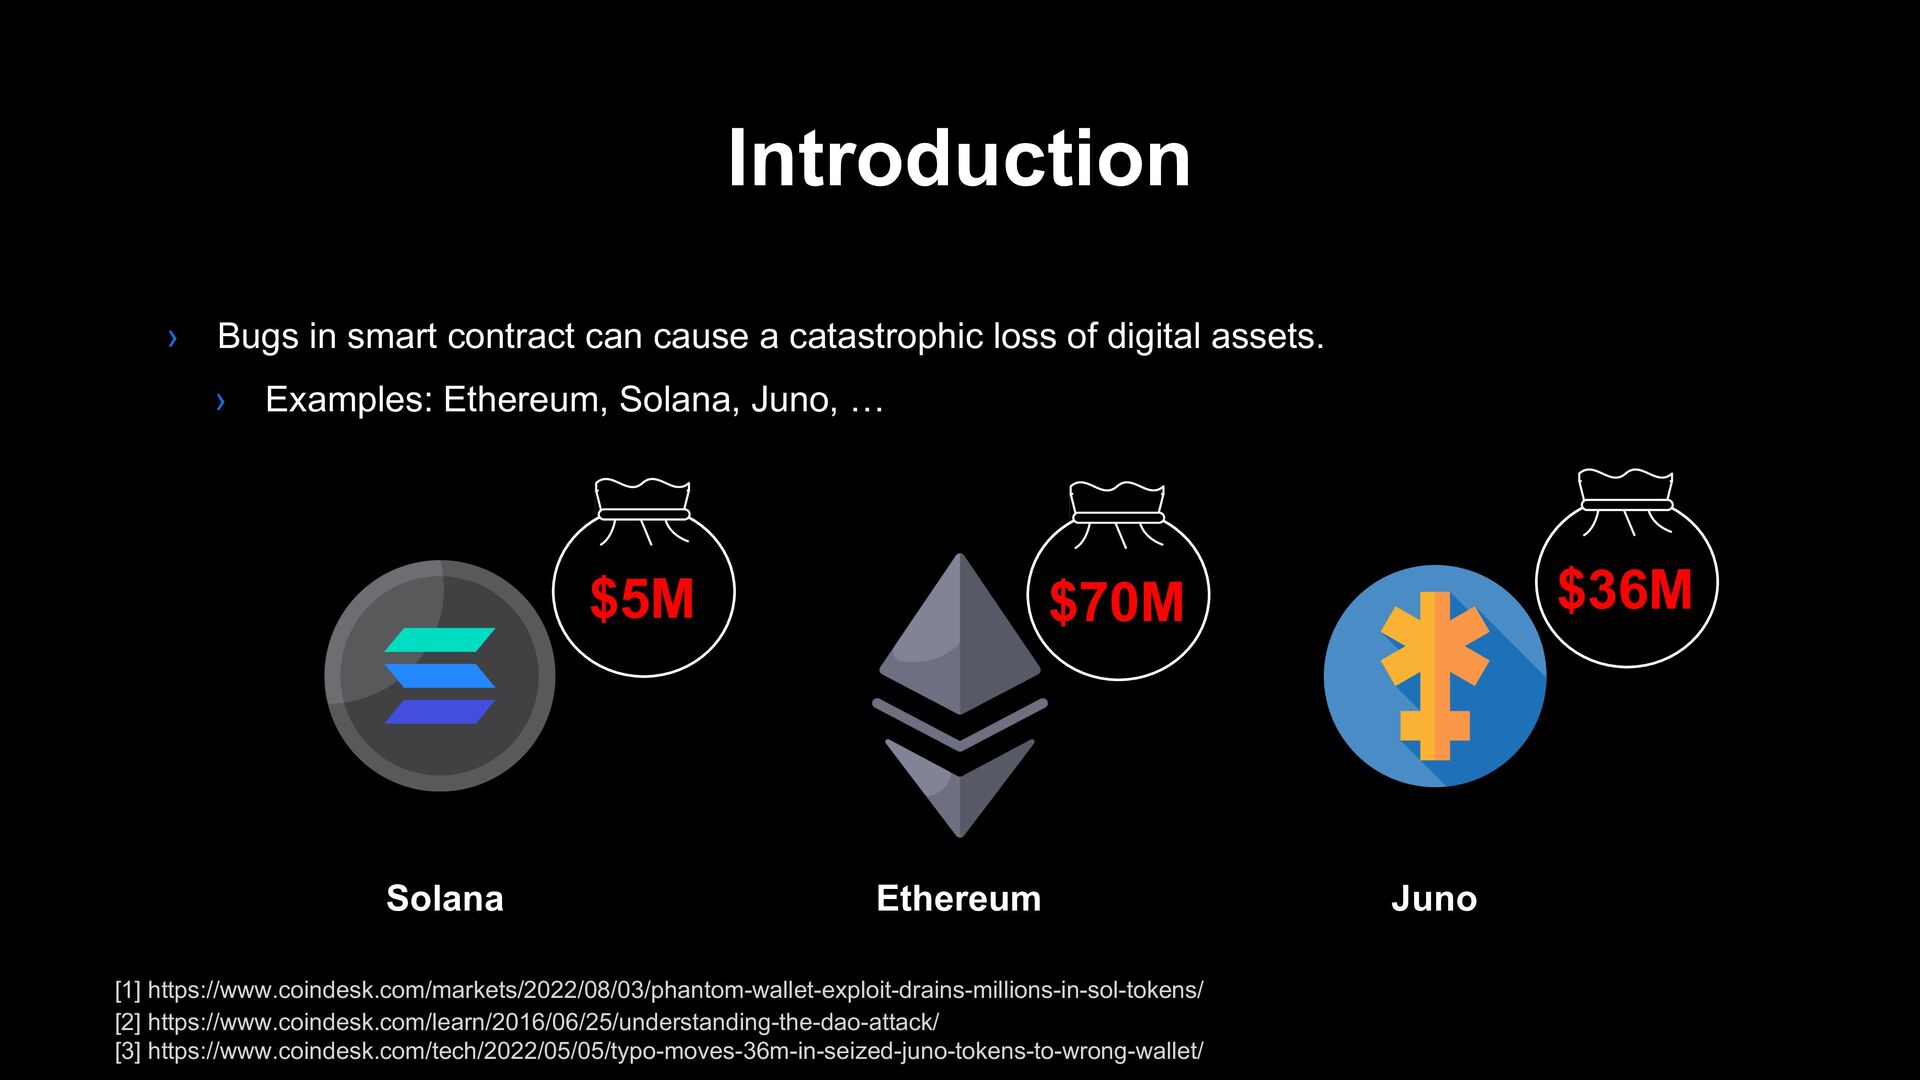
Introduction › Bugs in smart contract can cause a catastrophic
loss of digital assets. › Examples: Ethereum, Solana, Juno, … $5M Ethereum Solana Juno $70M $36M [1] https://www.coindesk.com/markets/2022/08/03/phantom-wallet-exploit-drains-millions-in-sol-tokens/ [2] https://www.coindesk.com/learn/2016/06/25/understanding-the-dao-attack/ [3] https://www.coindesk.com/tech/2022/05/05/typo-moves-36m-in-seized-juno-tokens-to-wrong-wallet/ -
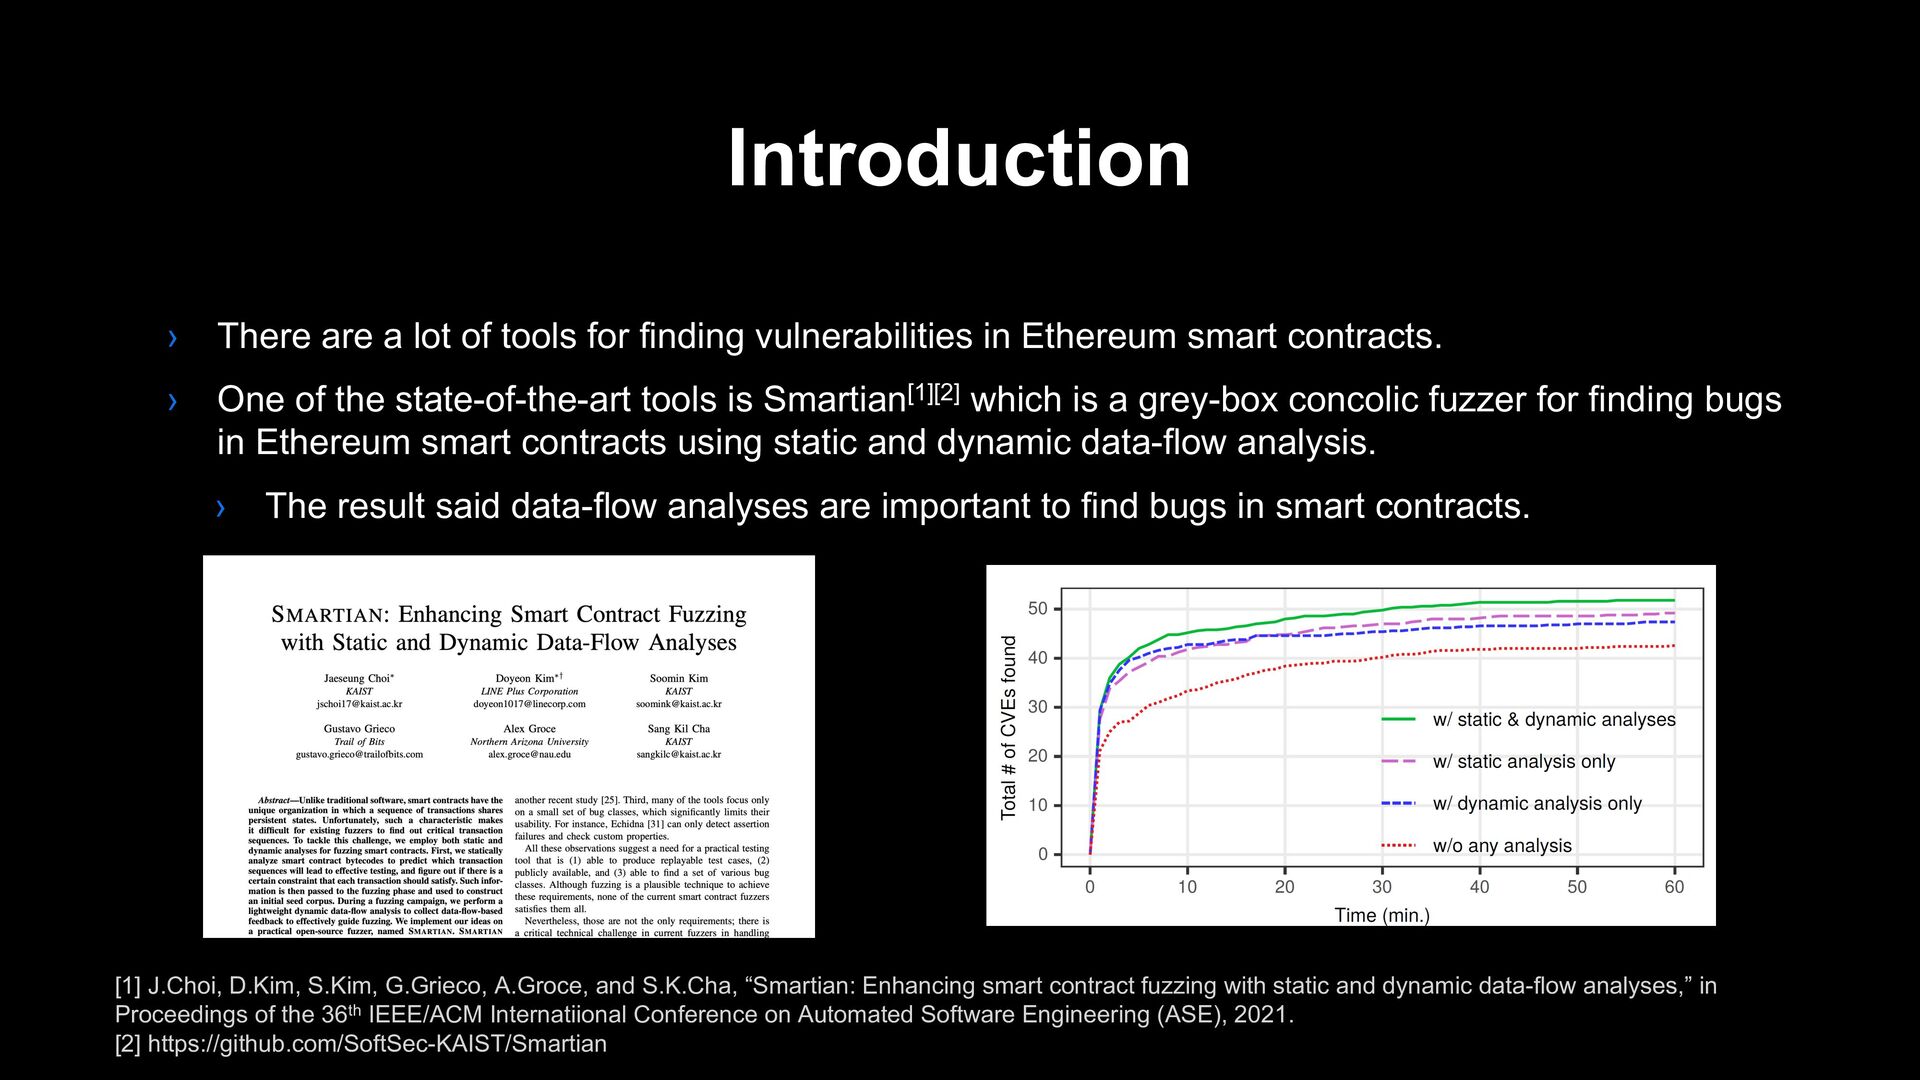
Introduction › There are a lot of tools for finding
vulnerabilities in Ethereum smart contracts. › One of the state-of-the-art tools is Smartian[1][2] which is a grey-box concolic fuzzer for finding bugs in Ethereum smart contracts using static and dynamic data-flow analysis. › The result said data-flow analyses are important to find bugs in smart contracts. [1] J.Choi, D.Kim, S.Kim, G.Grieco, A.Groce, and S.K.Cha, “Smartian: Enhancing smart contract fuzzing with static and dynamic data-flow analyses,” in Proceedings of the 36th IEEE/ACM Internatiional Conference on Automated Software Engineering (ASE), 2021. [2] https://github.com/SoftSec-KAIST/Smartian -
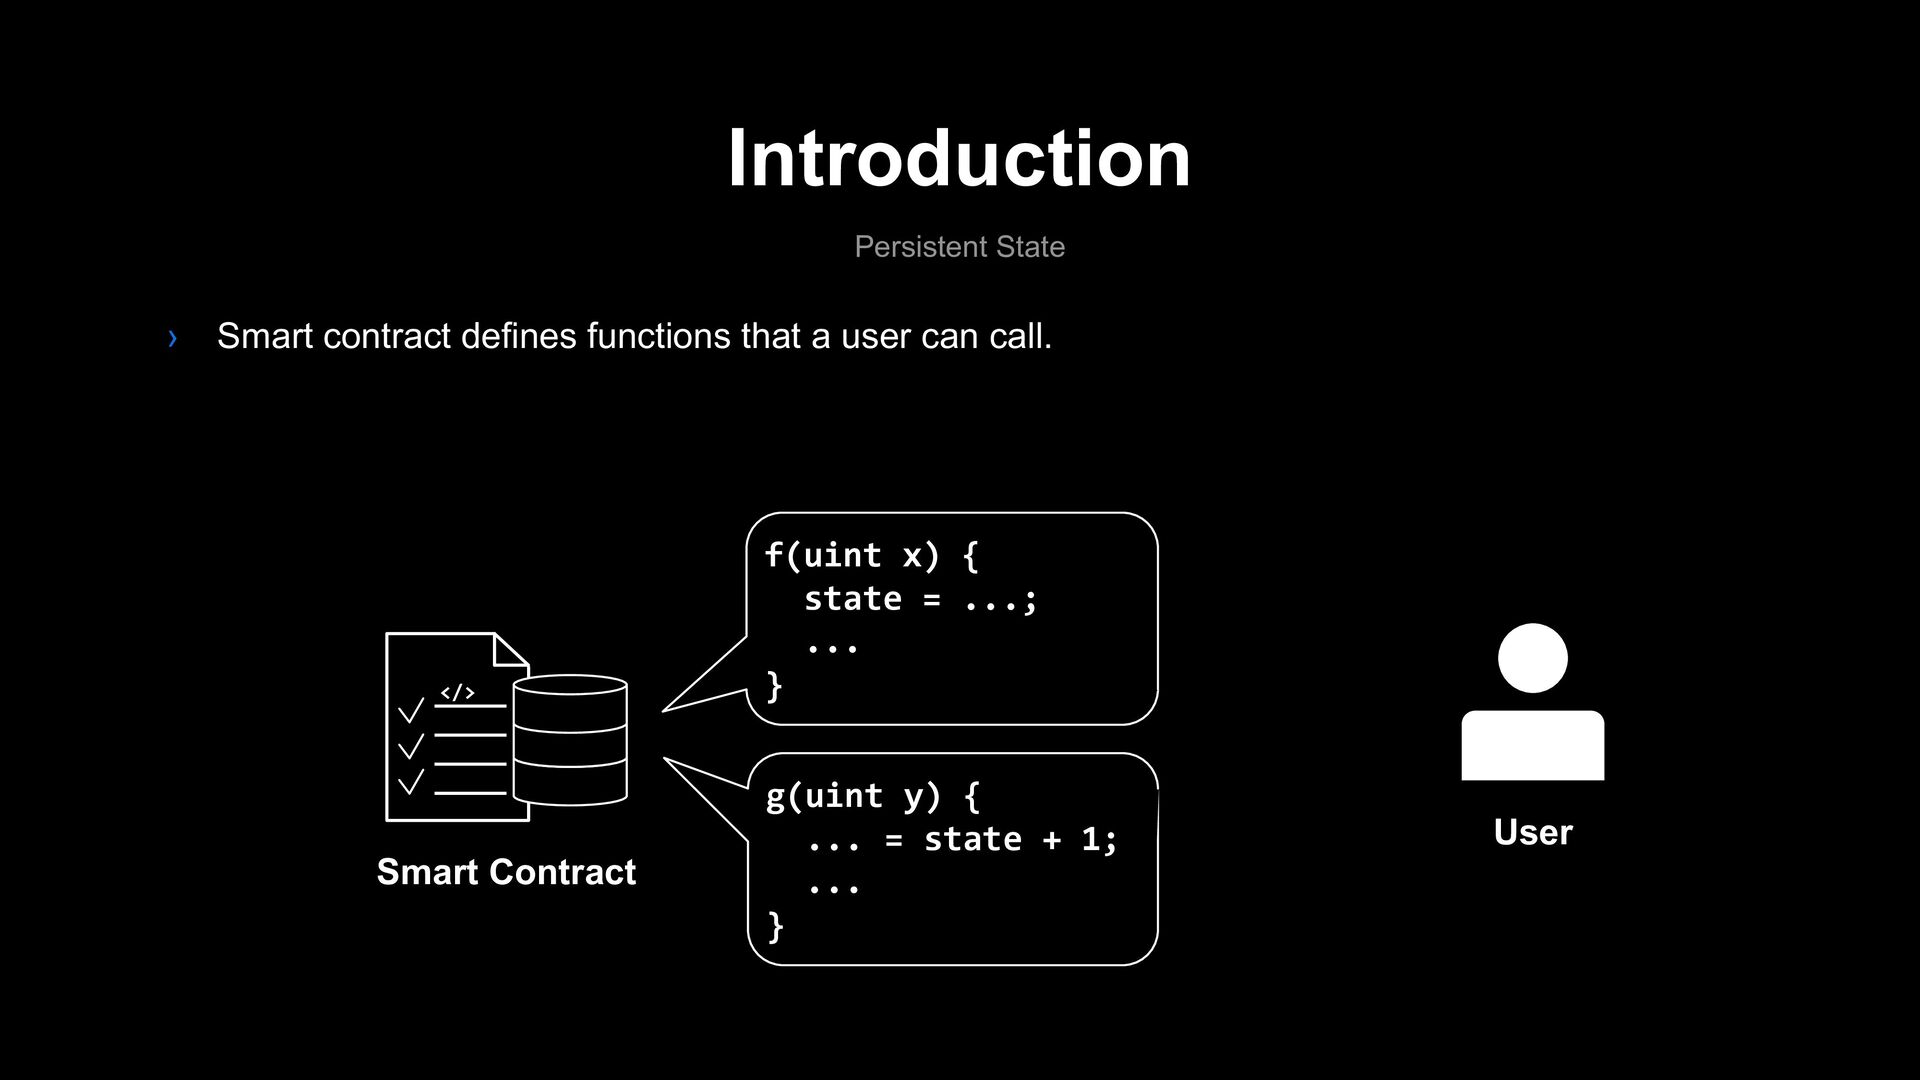
Introduction Persistent State g(uint y) { ... = state +
1; ... } f(uint x) { state = ...; ... } User </> Smart Contract › Smart contract defines functions that a user can call. -
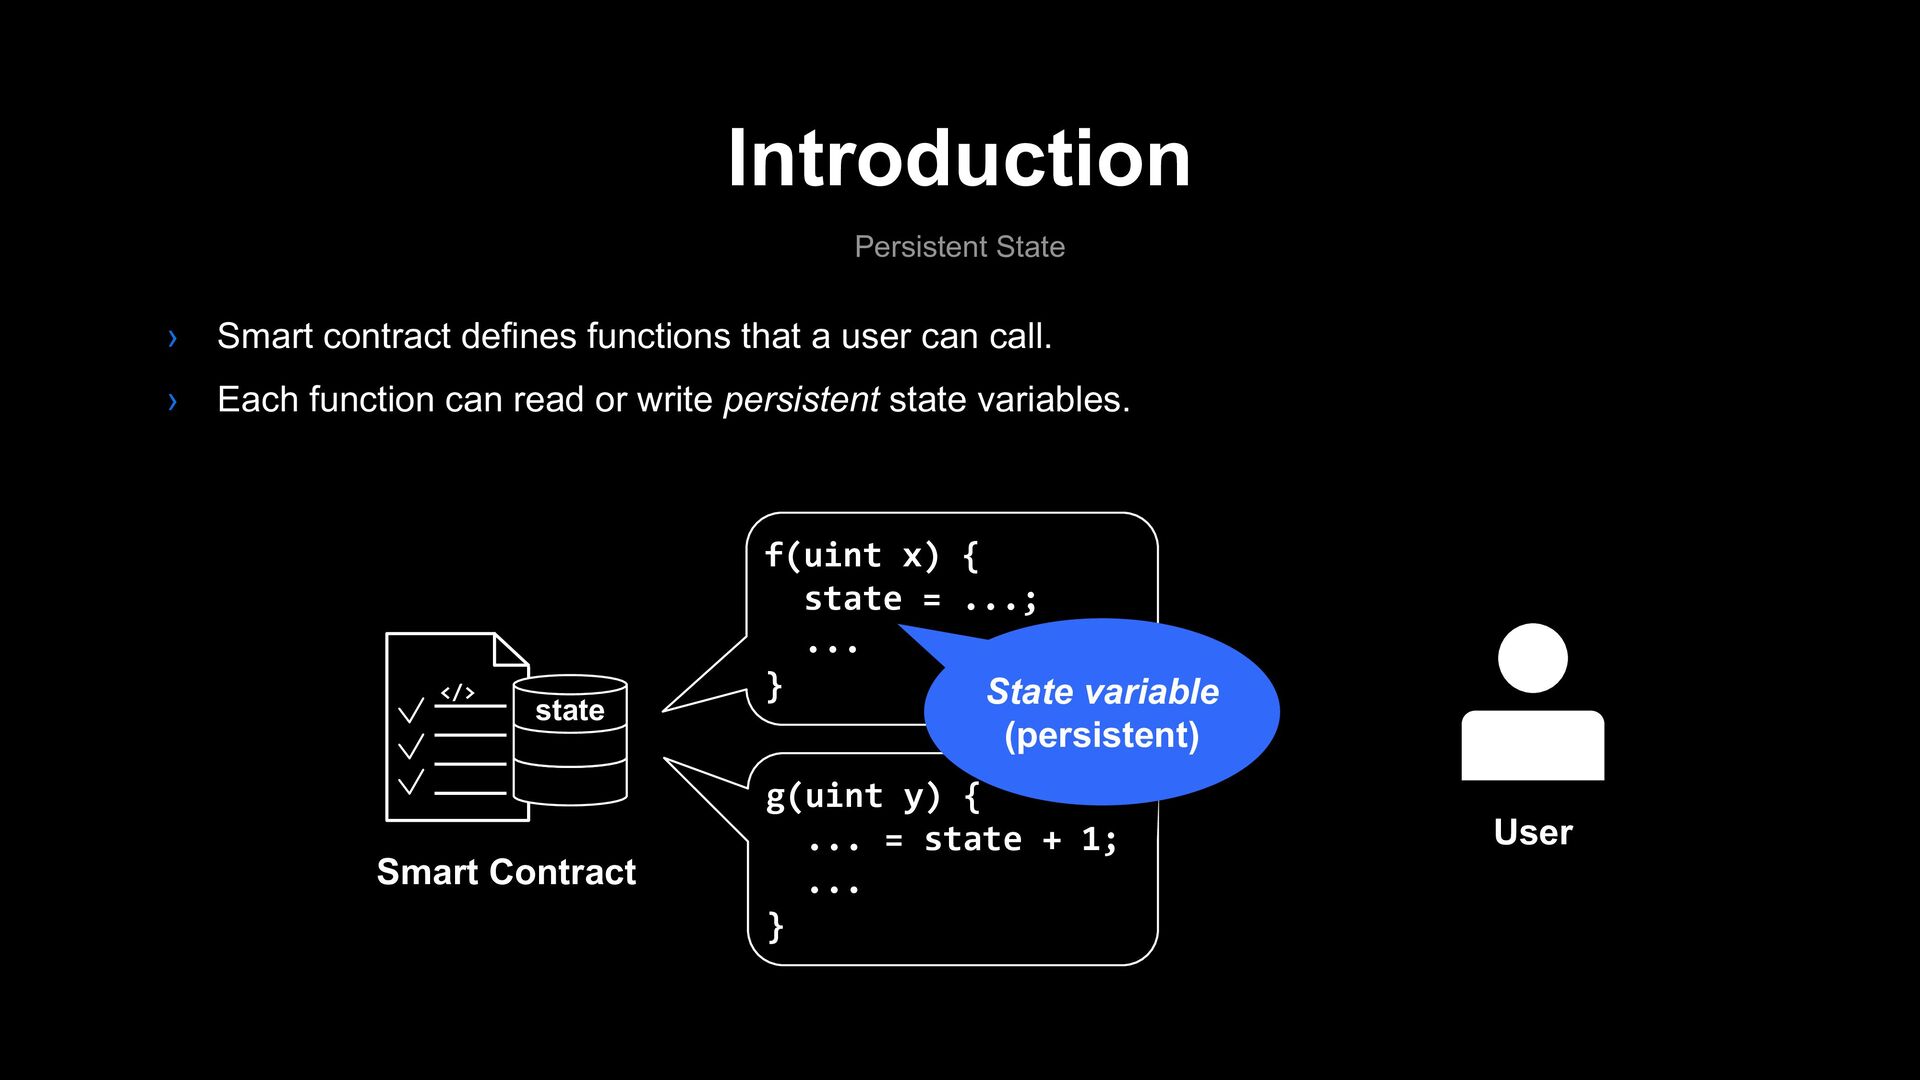
Introduction Persistent State g(uint y) { ... = state +
1; ... } f(uint x) { state = ...; ... } State variable (persistent) User </> state Smart Contract › Smart contract defines functions that a user can call. › Each function can read or write persistent state variables. -
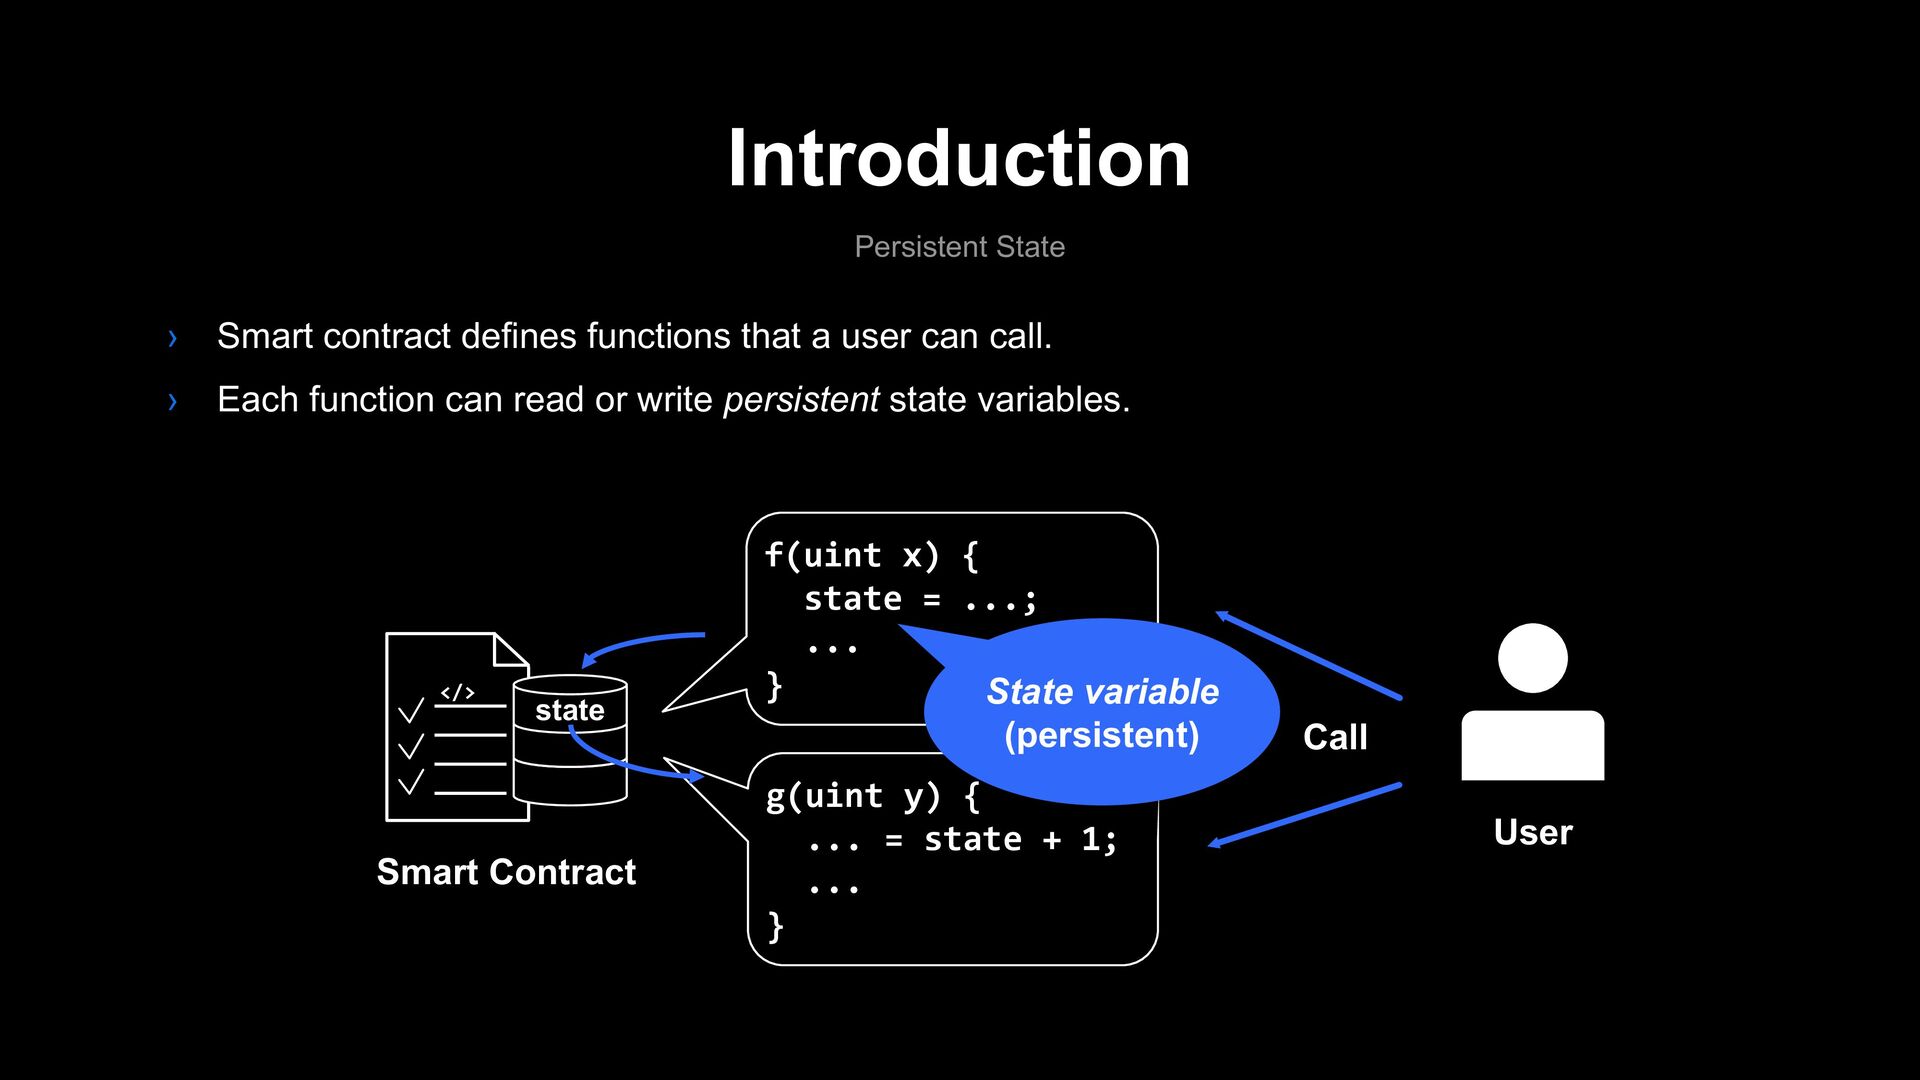
Introduction Persistent State g(uint y) { ... = state +
1; ... } f(uint x) { state = ...; ... } Call State variable (persistent) User </> state Smart Contract › Smart contract defines functions that a user can call. › Each function can read or write persistent state variables. -
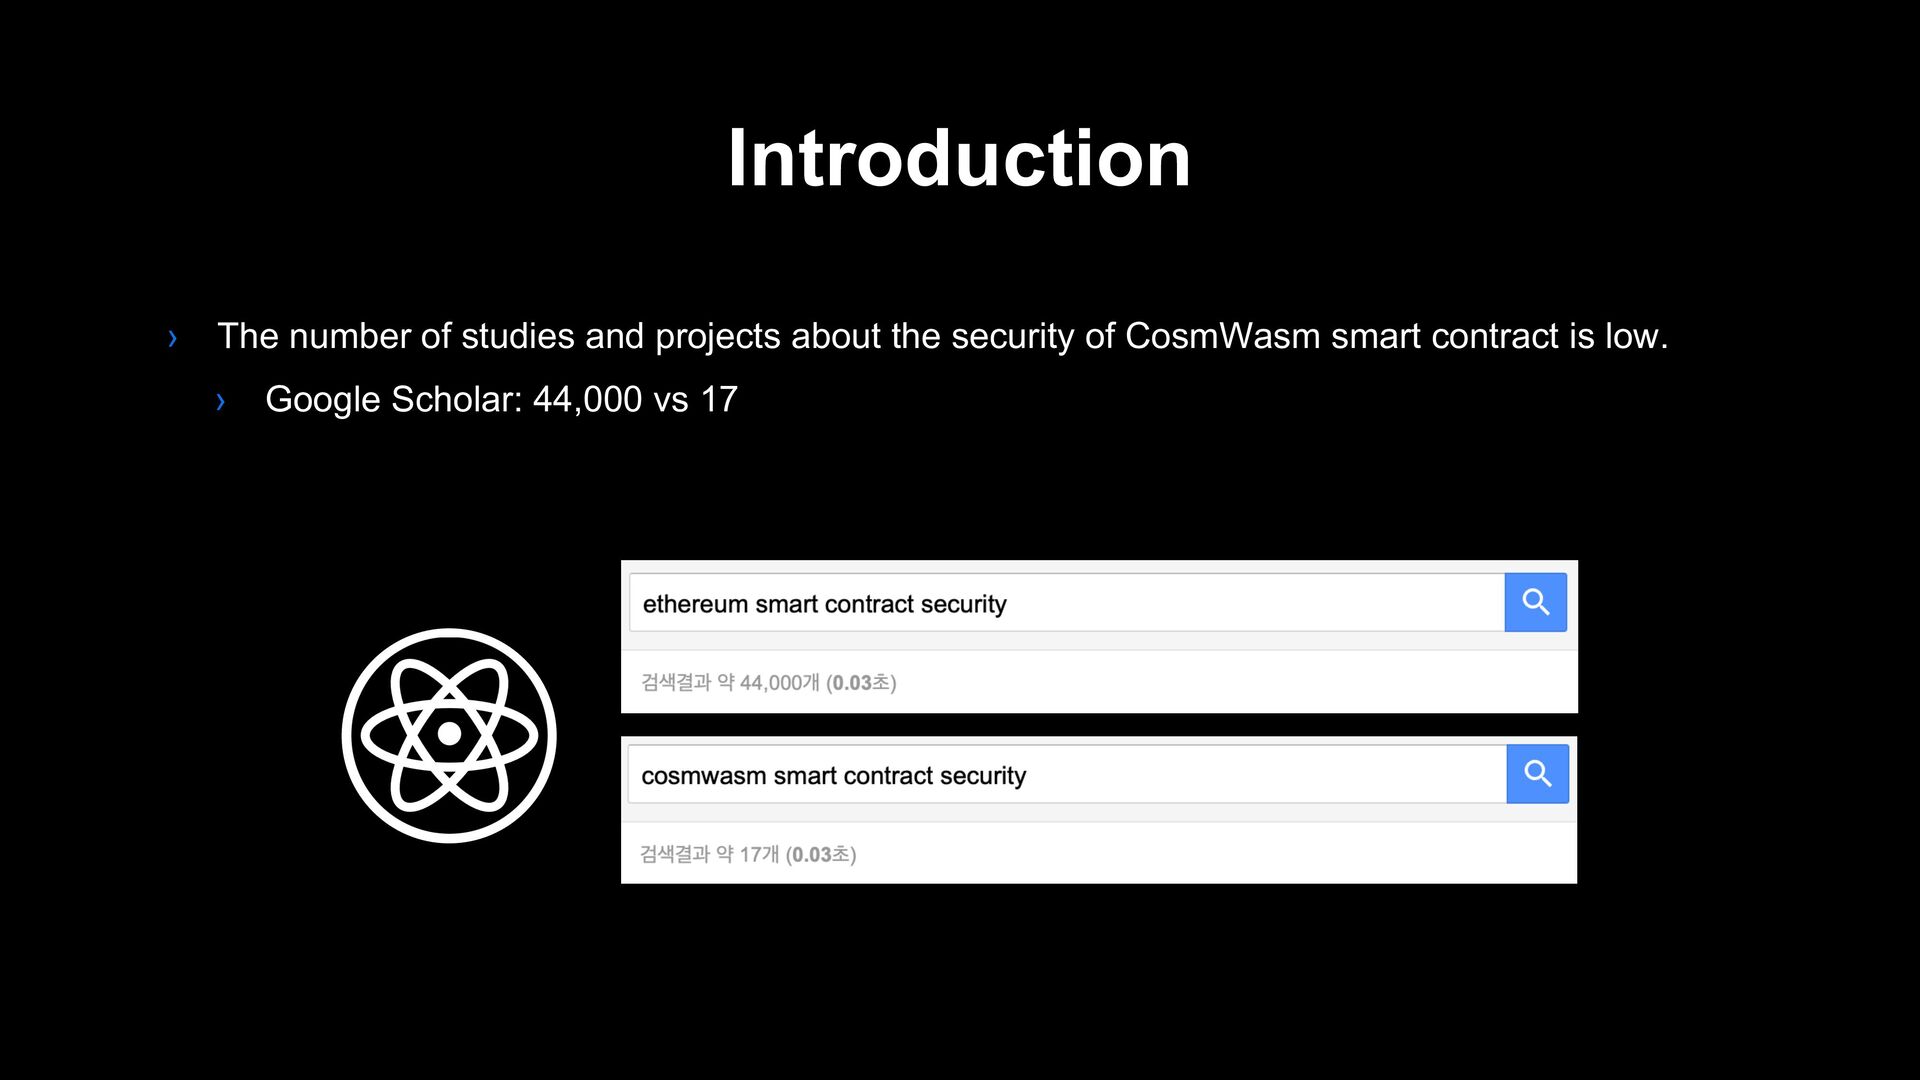
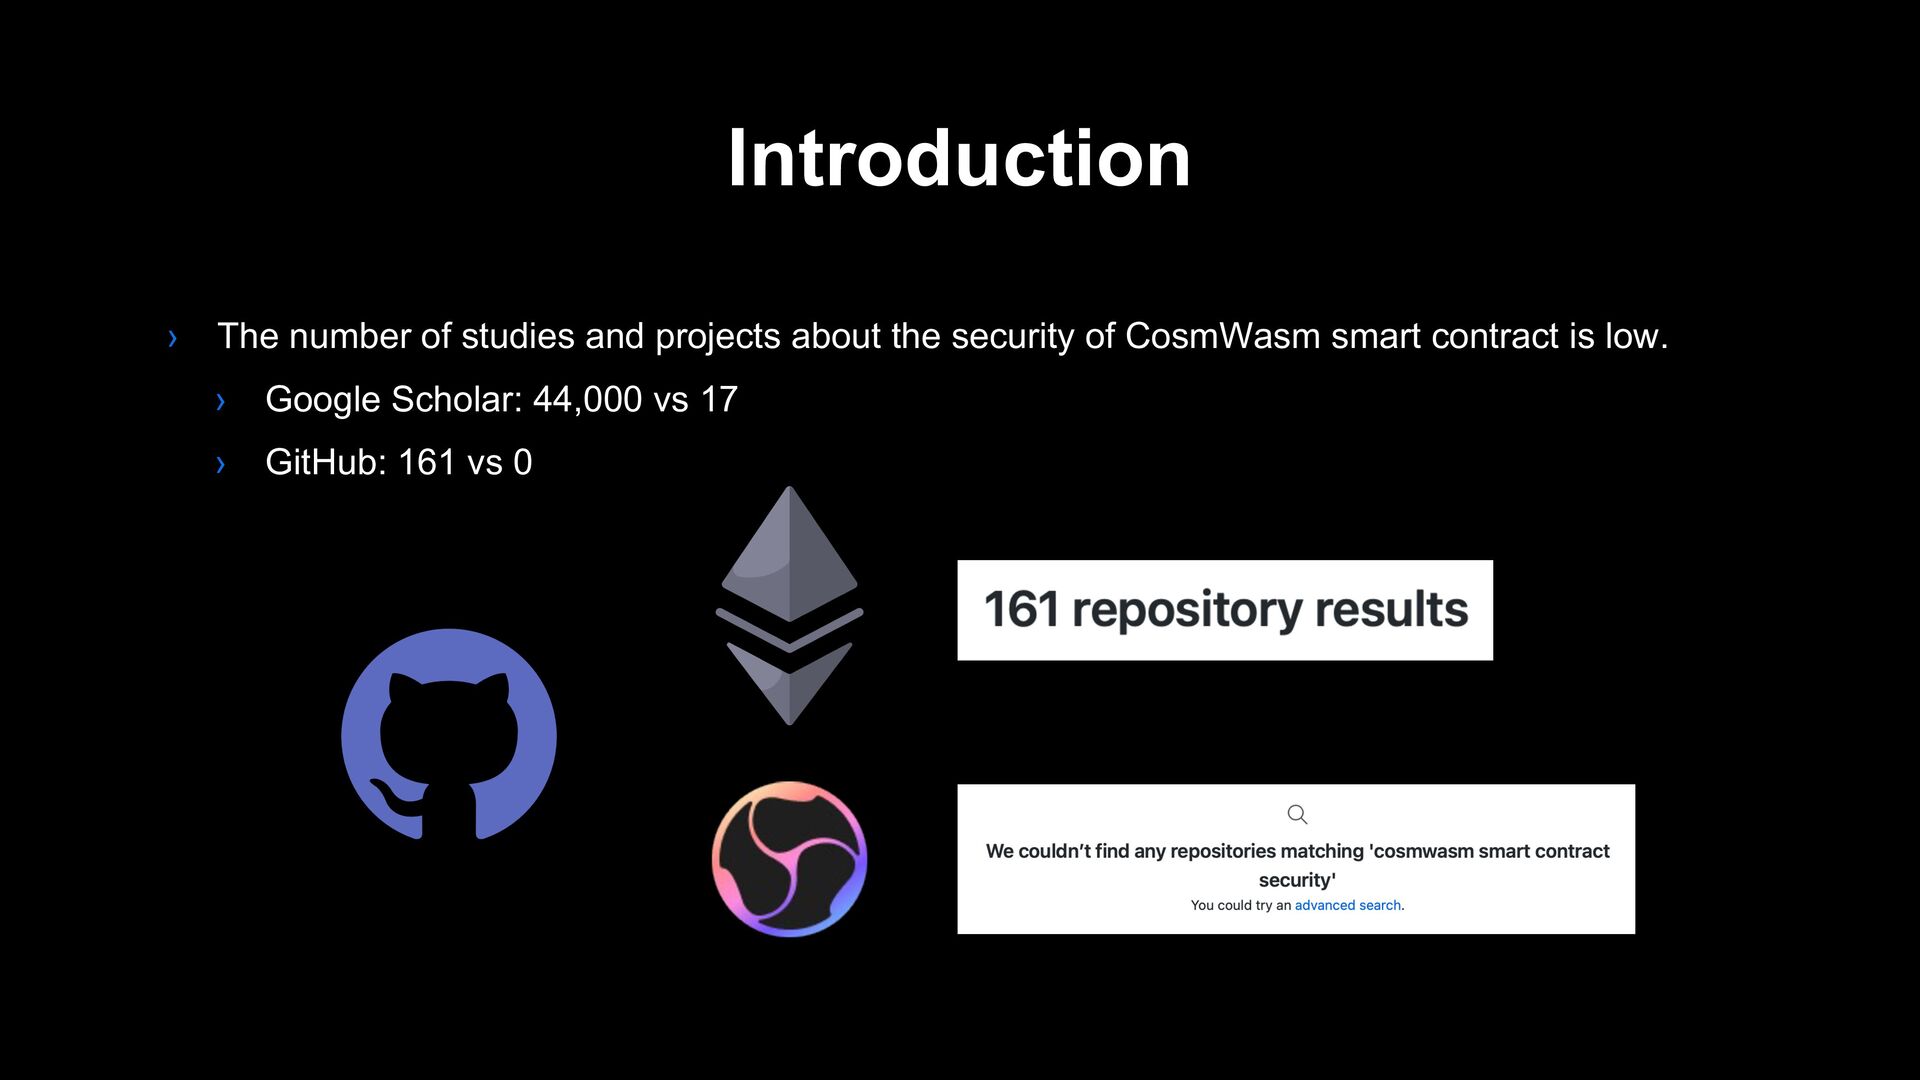
Introduction › The number of studies and projects about the
security of CosmWasm smart contract is low. › Google Scholar: 44,000 vs 17 -
Introduction › The number of studies and projects about the
security of CosmWasm smart contract is low. › Google Scholar: 44,000 vs 17 › GitHub: 161 vs 0 -
Introduction Summary › Recently, several bugs in the CosmWasm smart
contracts are discovered. › It’s important to find such bugs in the CosmWasm smart contracts as we expect the use of them to increase. › However, there is no open-sourced tool in order to find bugs in the CosmWasm smart contracts. Need to Make Testing Tool! -
How Bugs Can Occur? Outdated Vulnerable Module Used › Using
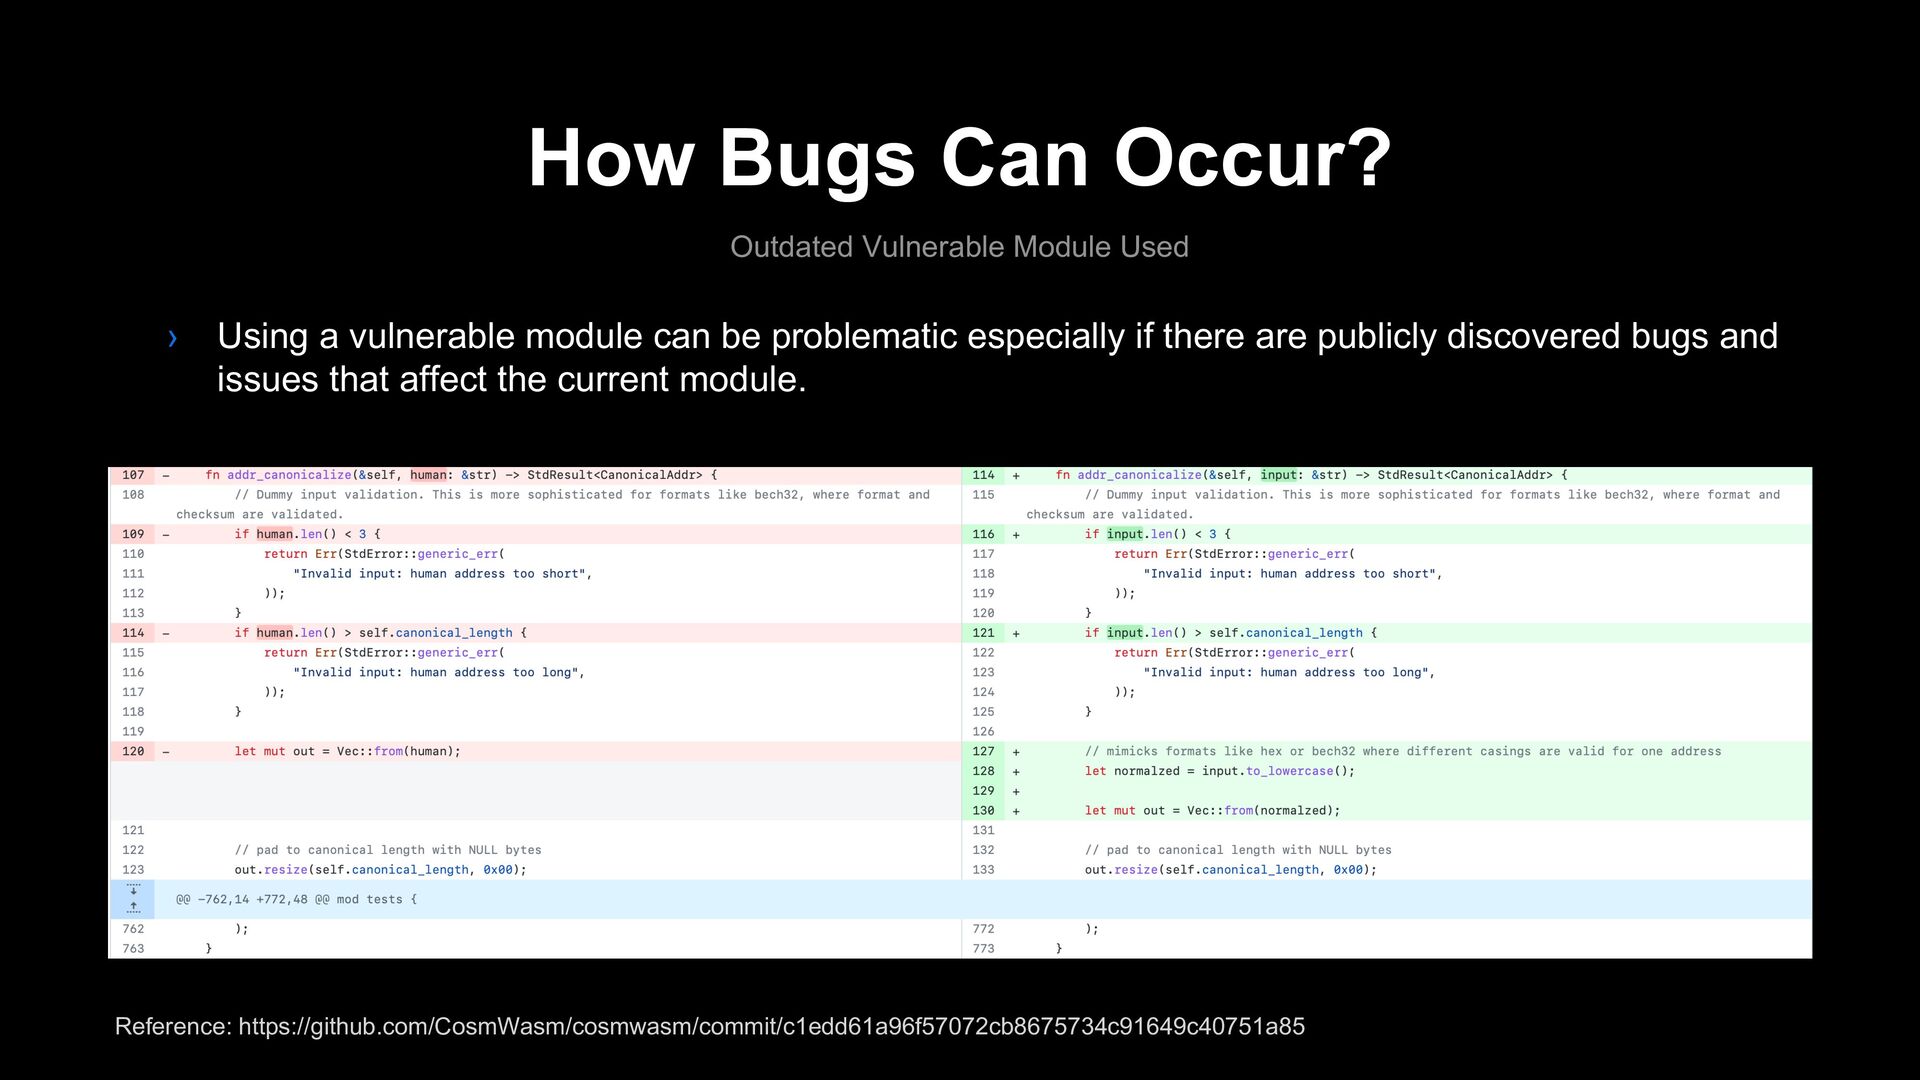
a vulnerable module can be problematic especially if there are publicly discovered bugs and issues that affect the current module. -
How Bugs Can Occur? Outdated Vulnerable Module Used › Using
a vulnerable module can be problematic especially if there are publicly discovered bugs and issues that affect the current module. Reference: https://github.com/CosmWasm/cosmwasm/commit/c1edd61a96f57072cb8675734c91649c40751a85 -
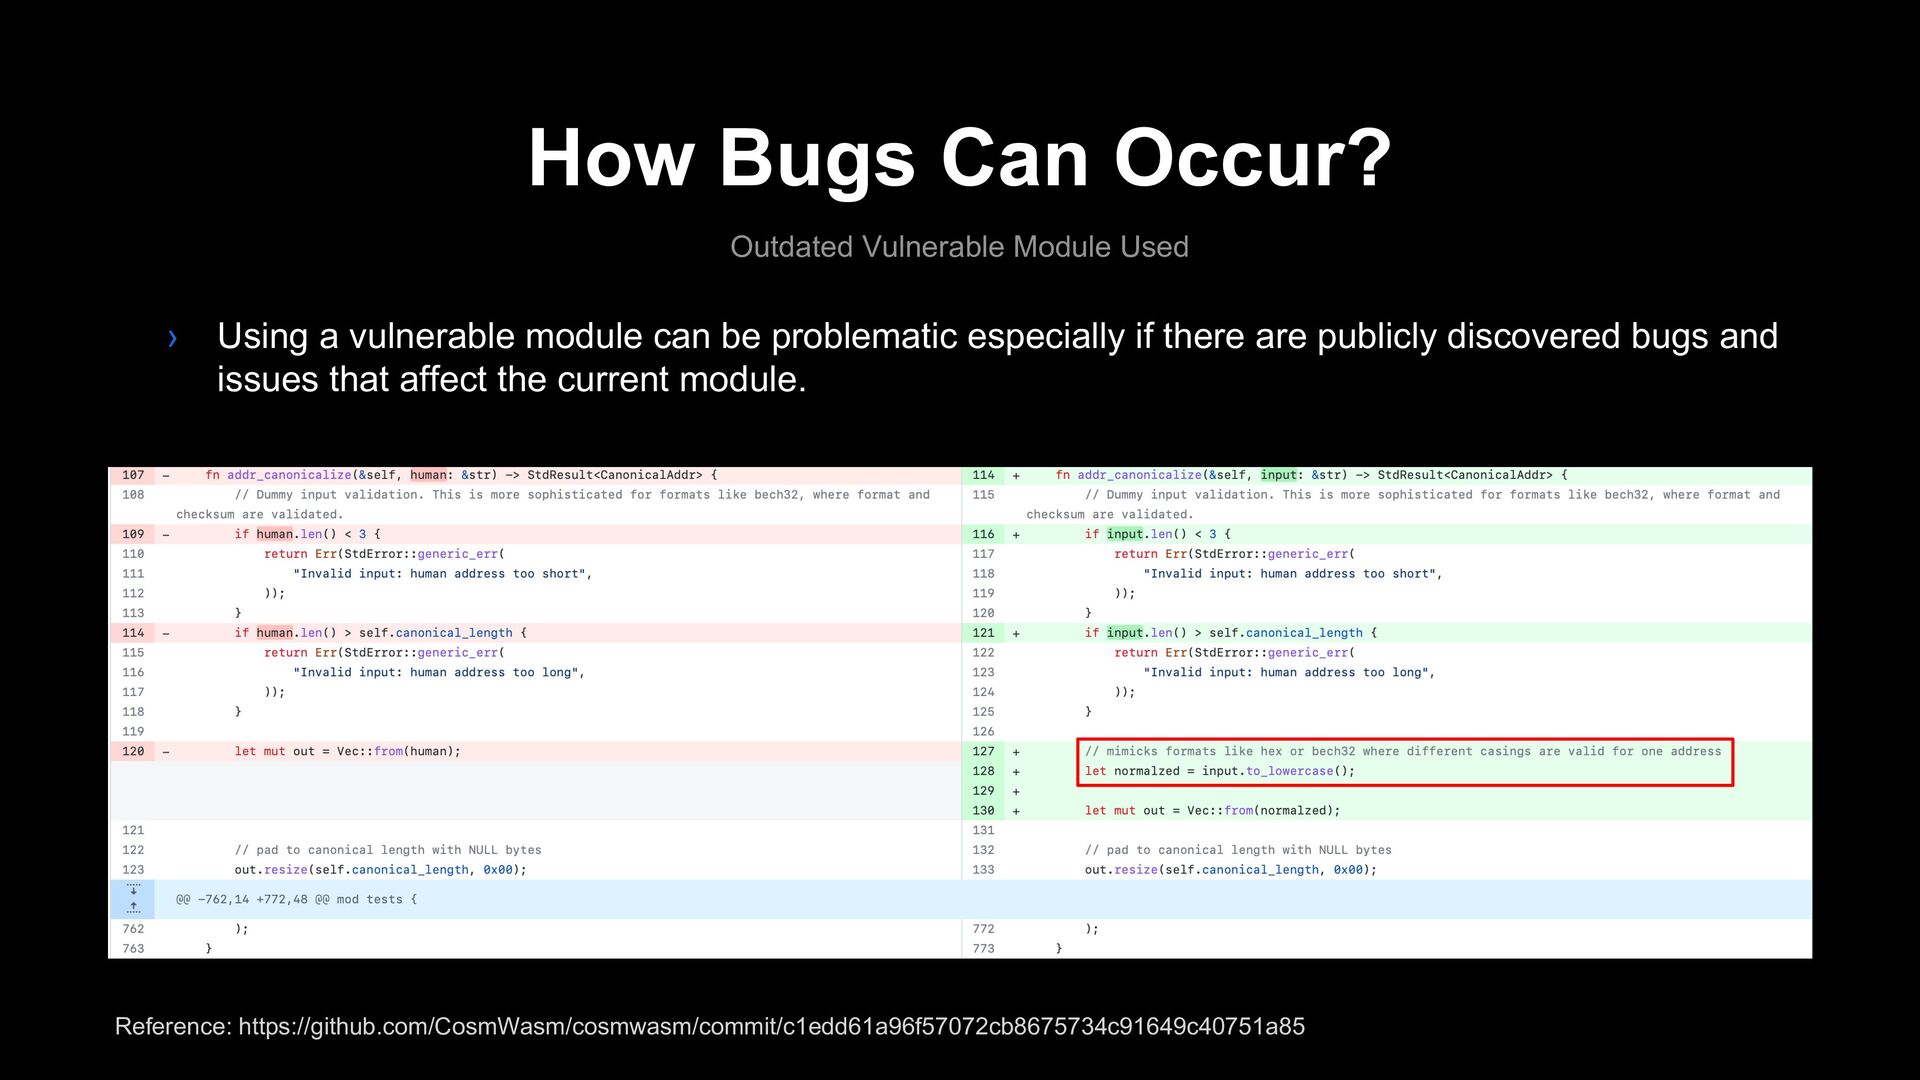
How Bugs Can Occur? Outdated Vulnerable Module Used › Using
a vulnerable module can be problematic especially if there are publicly discovered bugs and issues that affect the current module. Reference: https://github.com/CosmWasm/cosmwasm/commit/c1edd61a96f57072cb8675734c91649c40751a85 -
How Bugs Can Occur? Address Bypass › A smart contract
might wish to only access certain addresses, or not to access certain addresses. › If there is a problem in address check, a smart contract can allow unwanted addresses to access it. › ex: An attacker can receive all money in a smart contract. -
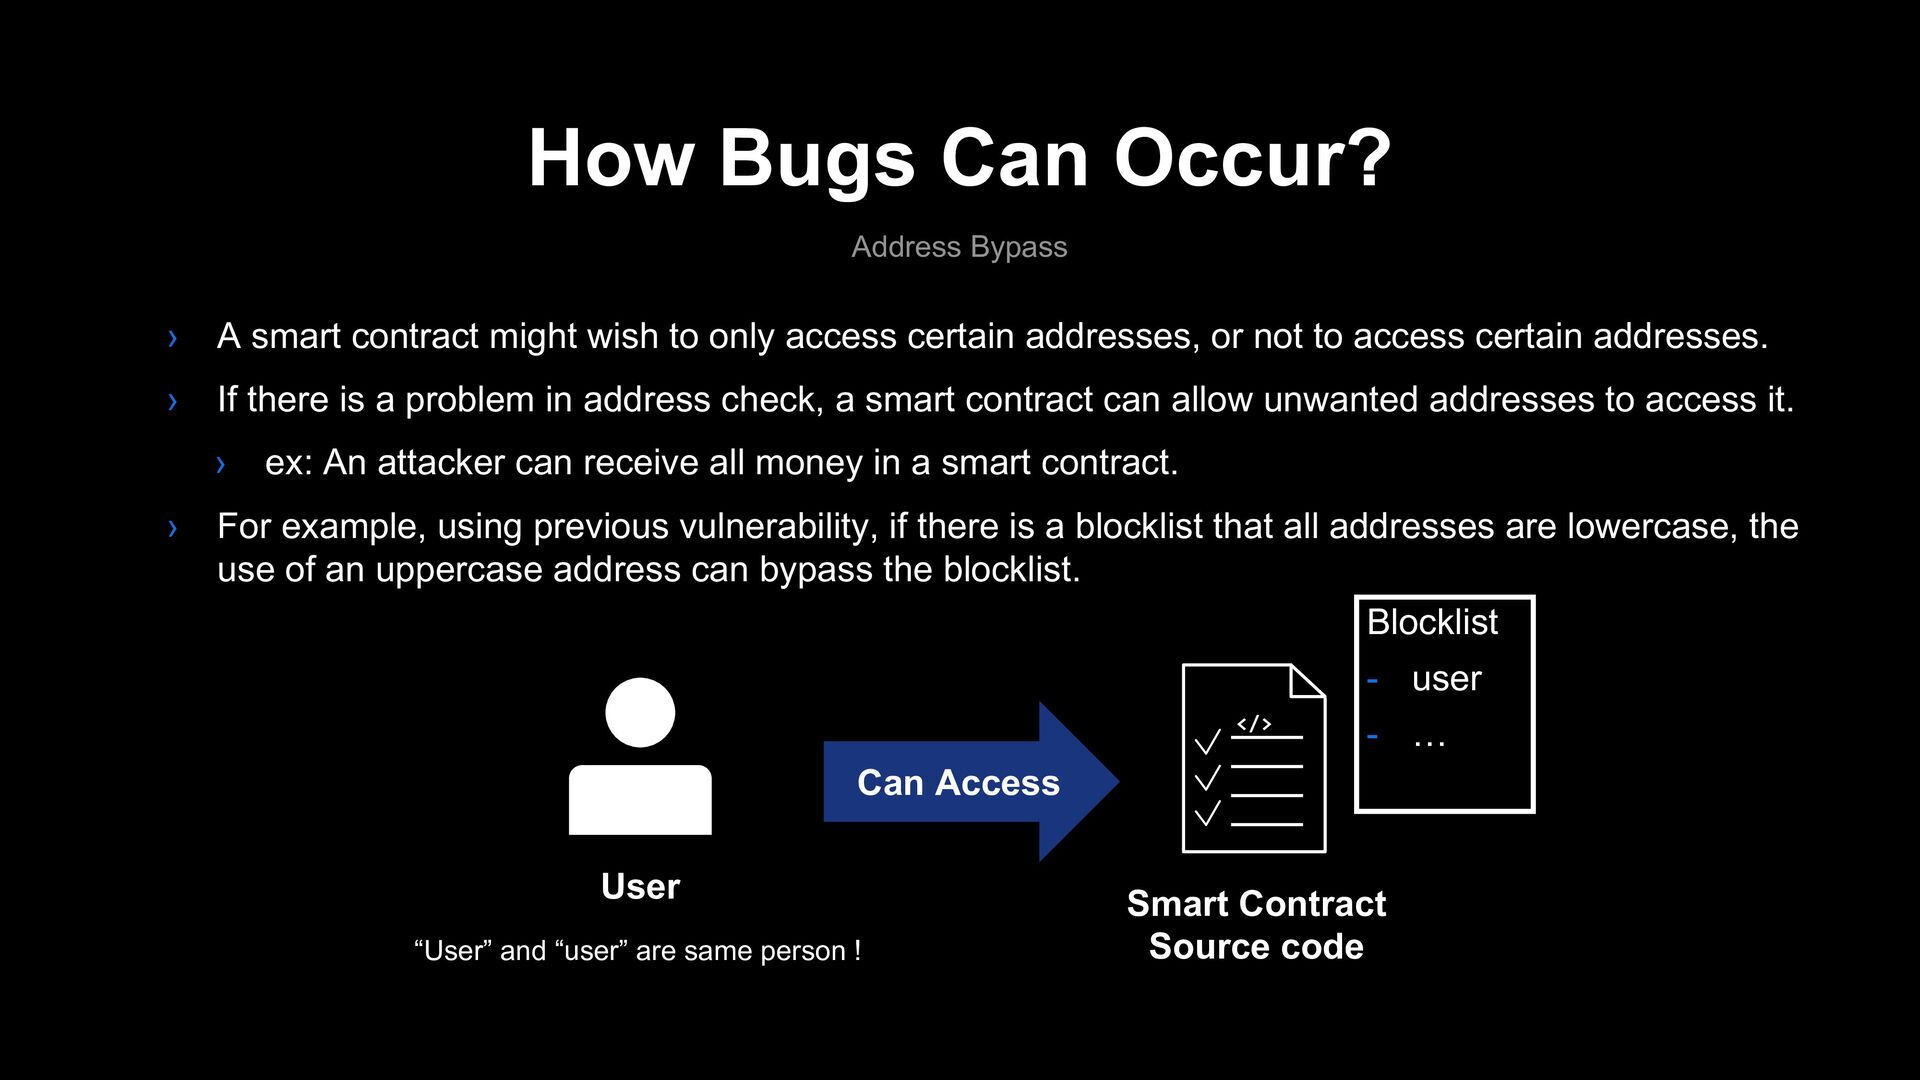
How Bugs Can Occur? Address Bypass › A smart contract
might wish to only access certain addresses, or not to access certain addresses. › If there is a problem in address check, a smart contract can allow unwanted addresses to access it. › ex: An attacker can receive all money in a smart contract. › For example, using previous vulnerability, if there is a blocklist that all addresses are lowercase, the use of an uppercase address can bypass the blocklist. User </> Smart Contract Source code Blocklist - user - … “User” and “user” are same person ! Can Access -
How Bugs Can Occur? Integer-Related Bugs › When integer overflow
or underflow occurs, a panic!() occur. › In the case of Ethereum smart contract, when integer overflow/underflow occurs, the value is also overflowed/underflowed without error. -
How Bugs Can Occur? Integer-Related Bugs › When integer overflow
or underflow occurs, a panic!() occur. › In the case of Ethereum smart contract, when integer overflow/underflow occurs, the value is also overflowed/underflowed without error. › When you try integer type conversion using into() or try_into(), type conversion error can occur. -
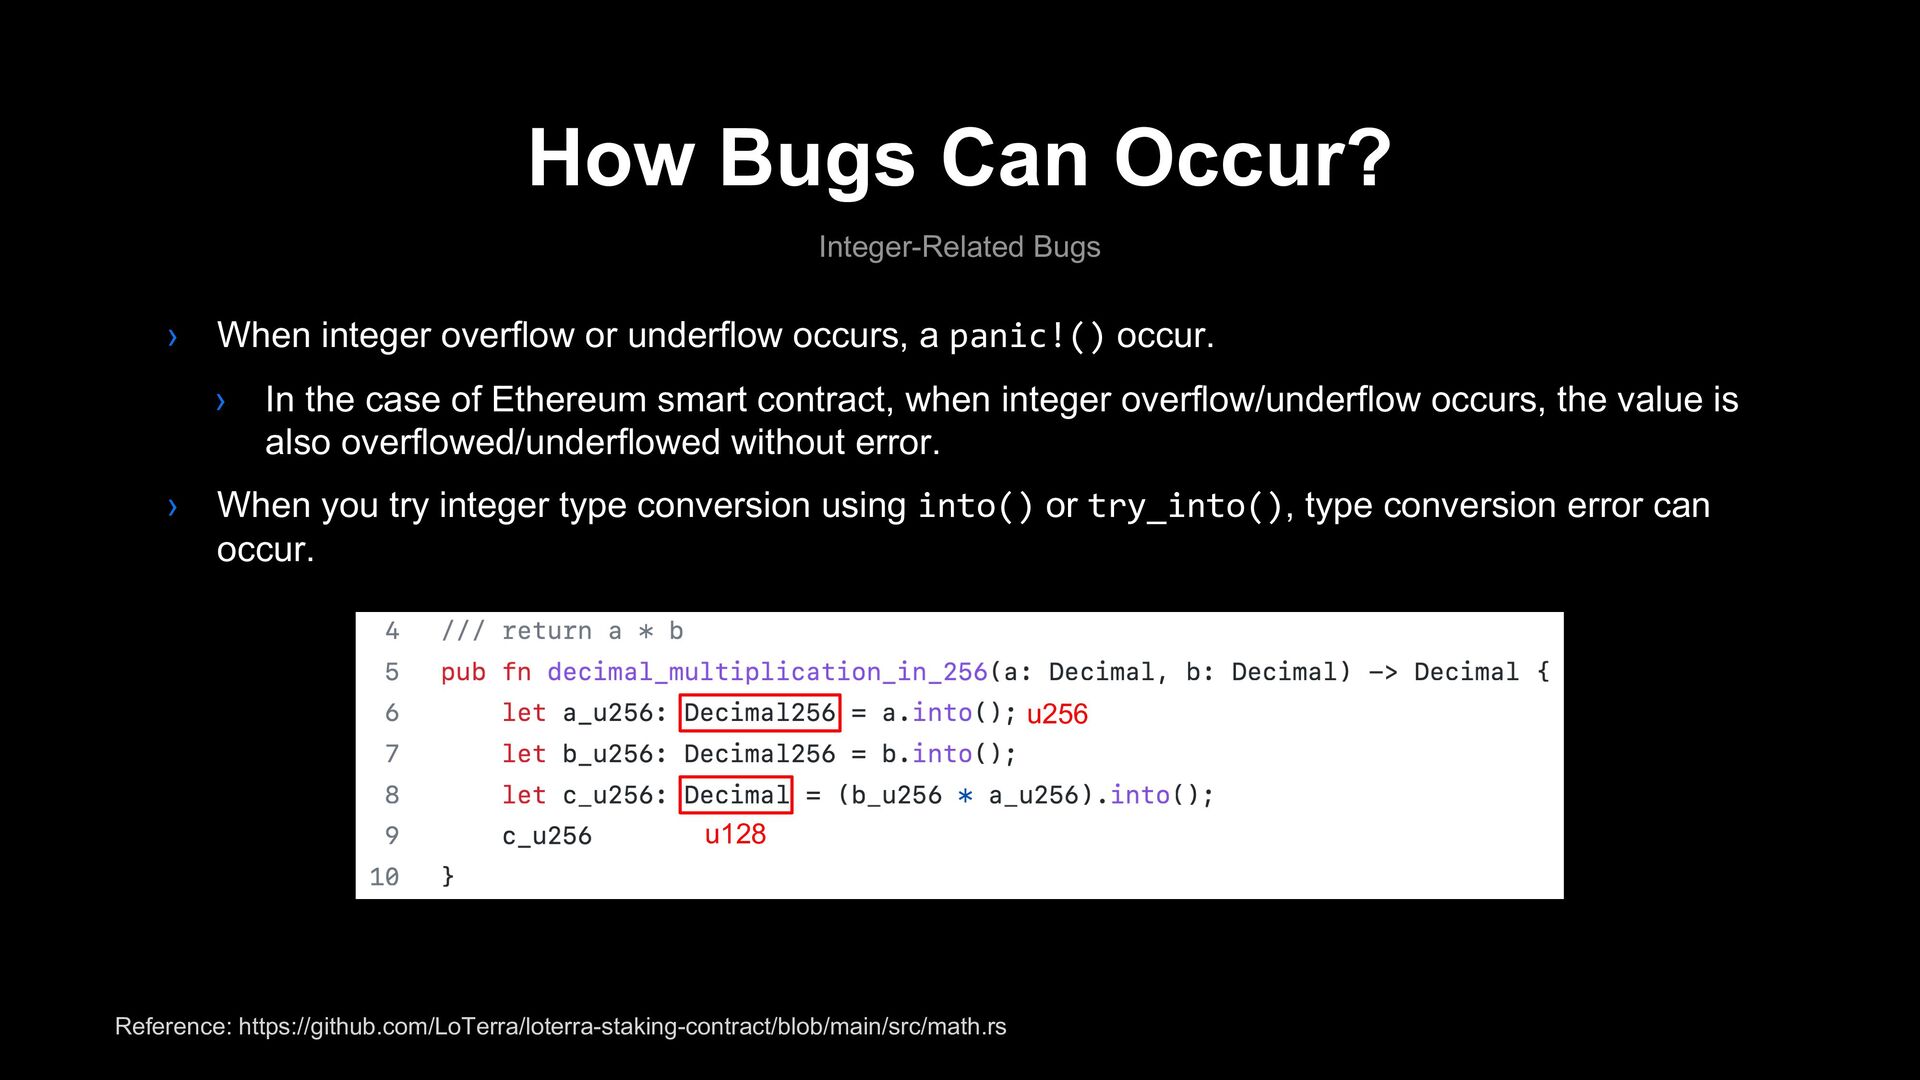
How Bugs Can Occur? Integer-Related Bugs › When integer overflow
or underflow occurs, a panic!() occur. › In the case of Ethereum smart contract, when integer overflow/underflow occurs, the value is also overflowed/underflowed without error. › When you try integer type conversion using into() or try_into(), type conversion error can occur. Reference: https://github.com/LoTerra/loterra-staking-contract/blob/main/src/math.rs u128 u256 -
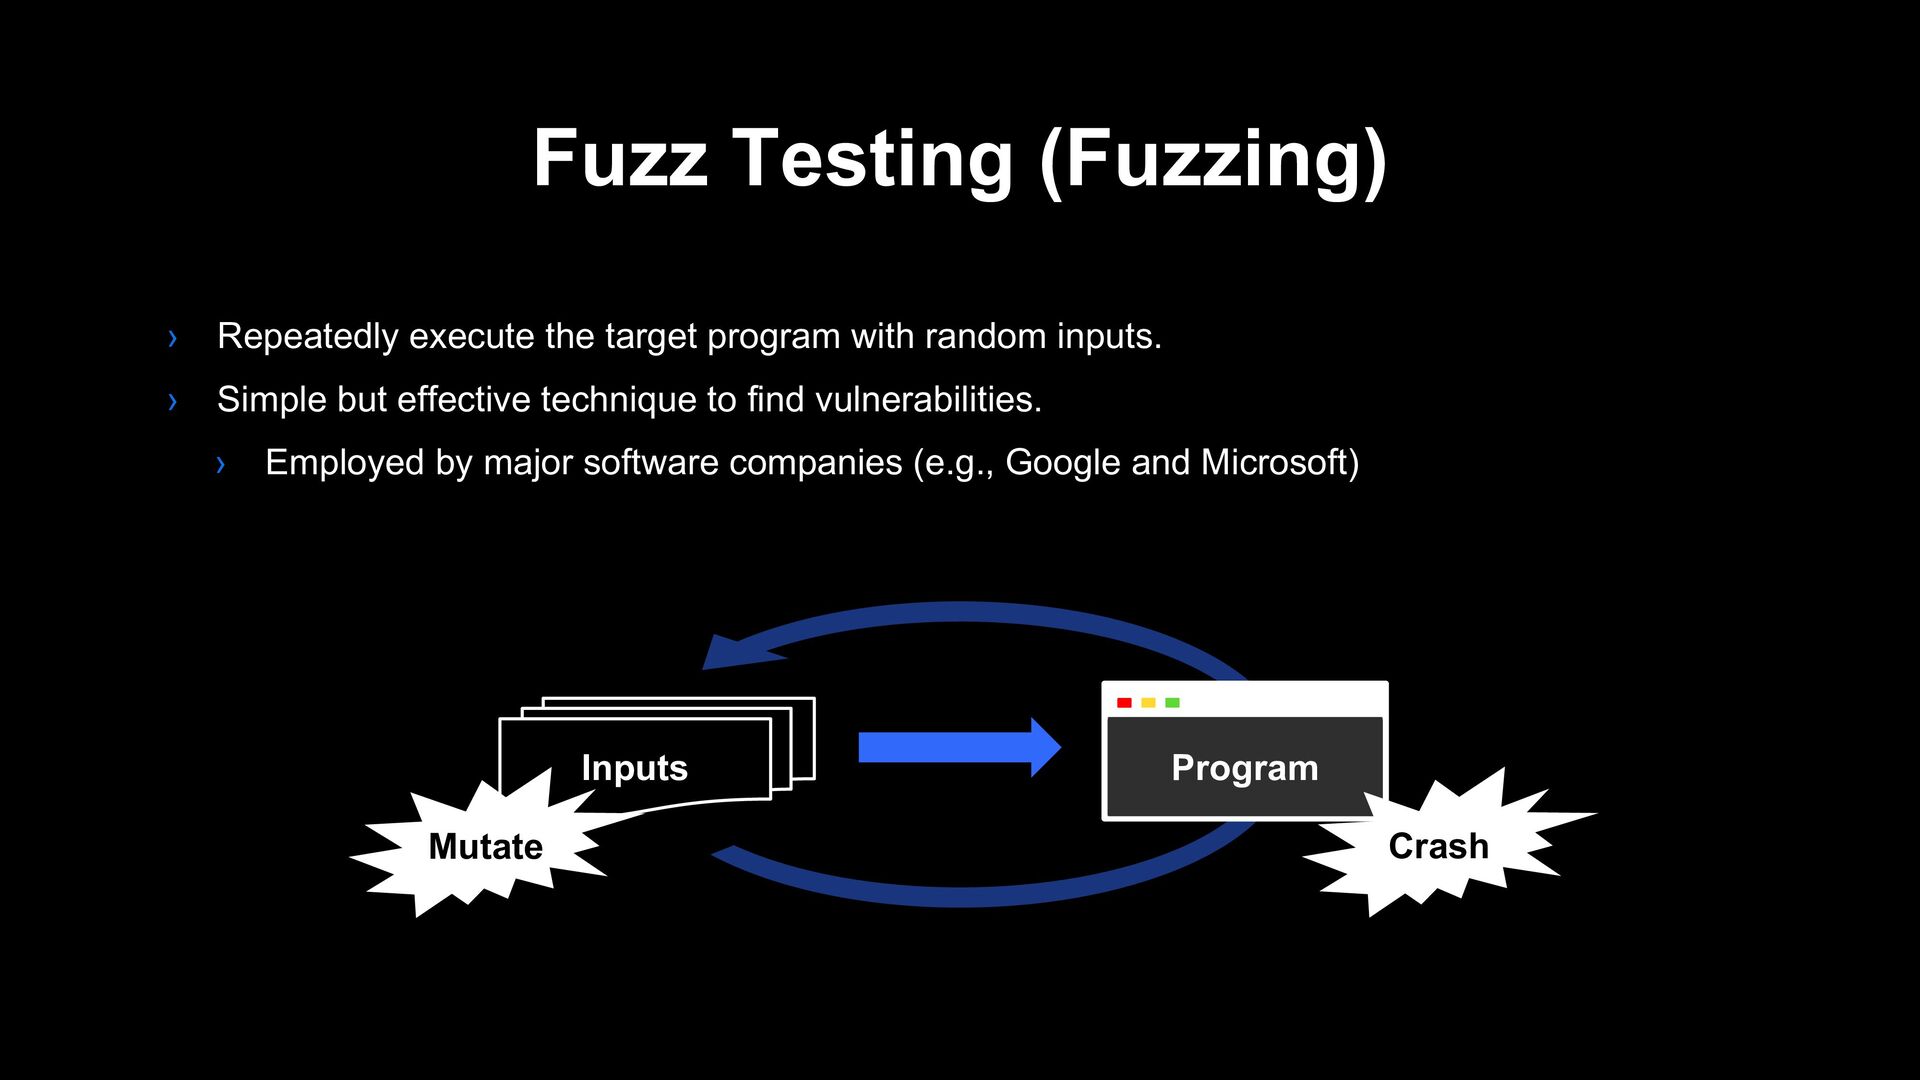
Fuzz Testing (Fuzzing) › Repeatedly execute the target program with
random inputs. › Simple but effective technique to find vulnerabilities. › Employed by major software companies (e.g., Google and Microsoft) Inputs Program Crash Mutate -
Challenges › There is no open-sourced bug-finder for CosmWasm smart
contract. › There is no tool to instrument the data-flow for CosmWasm smart contract as far as we know. › Tracking data-flow for state is important to bugs in smart contracts[1]. [1] J.Choi, D.Kim, S.Kim, G.Grieco, A.Groce, and S.K.Cha, “Smartian: Enhancing smart contract fuzzing with static and dynamic data-flow analyses,” in Proceedings of the 36th IEEE/ACM Internatiional Conference on Automated Software Engineering (ASE), 2021. -
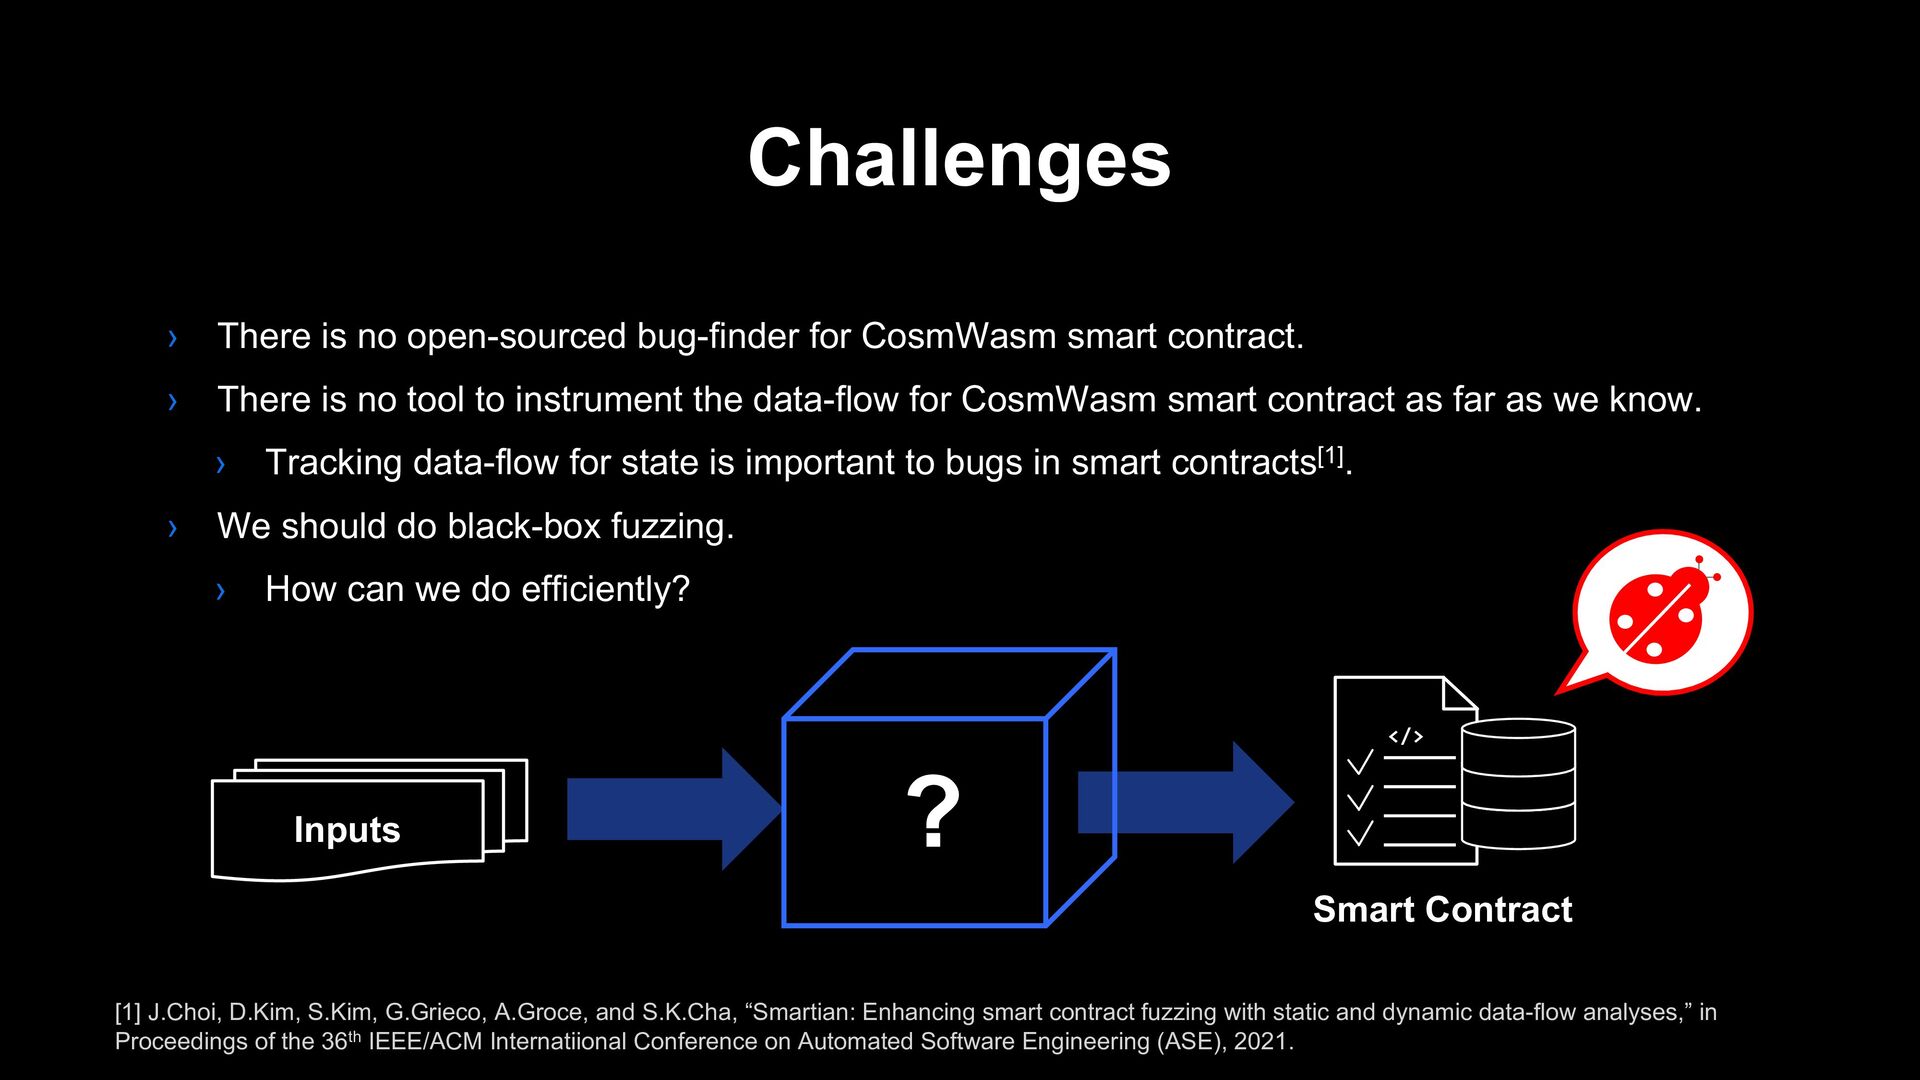
Challenges › There is no open-sourced bug-finder for CosmWasm smart
contract. › There is no tool to instrument the data-flow for CosmWasm smart contract as far as we know. › Tracking data-flow for state is important to bugs in smart contracts[1]. › We should do black-box fuzzing. › How can we do efficiently? [1] J.Choi, D.Kim, S.Kim, G.Grieco, A.Groce, and S.K.Cha, “Smartian: Enhancing smart contract fuzzing with static and dynamic data-flow analyses,” in Proceedings of the 36th IEEE/ACM Internatiional Conference on Automated Software Engineering (ASE), 2021. Inputs </> Smart Contract ? -
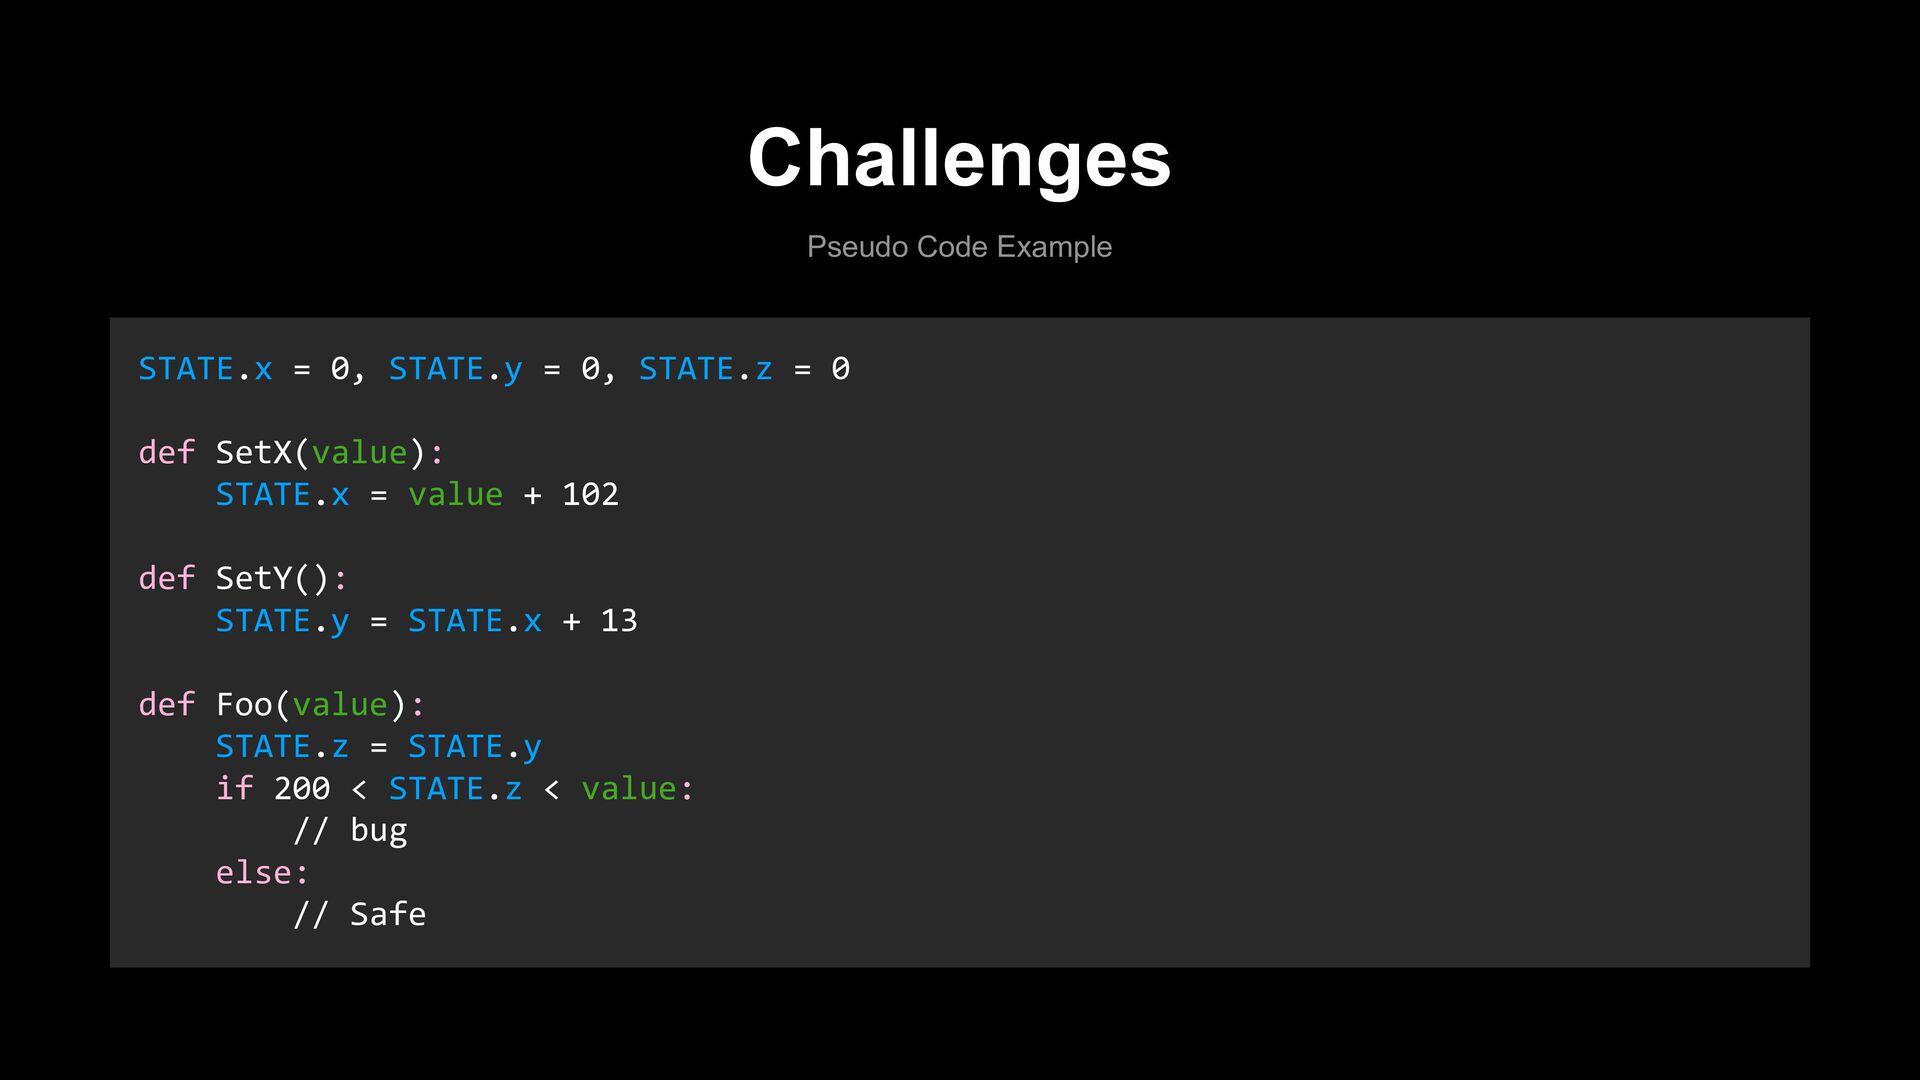
Challenges Pseudo Code Example STATE.x = 0, STATE.y = 0,
STATE.z = 0 def SetX(value): STATE.x = value + 102 def SetY(): STATE.y = STATE.x + 13 def Foo(value): STATE.z = STATE.y if 200 < STATE.z < value: // bug else: // Safe -
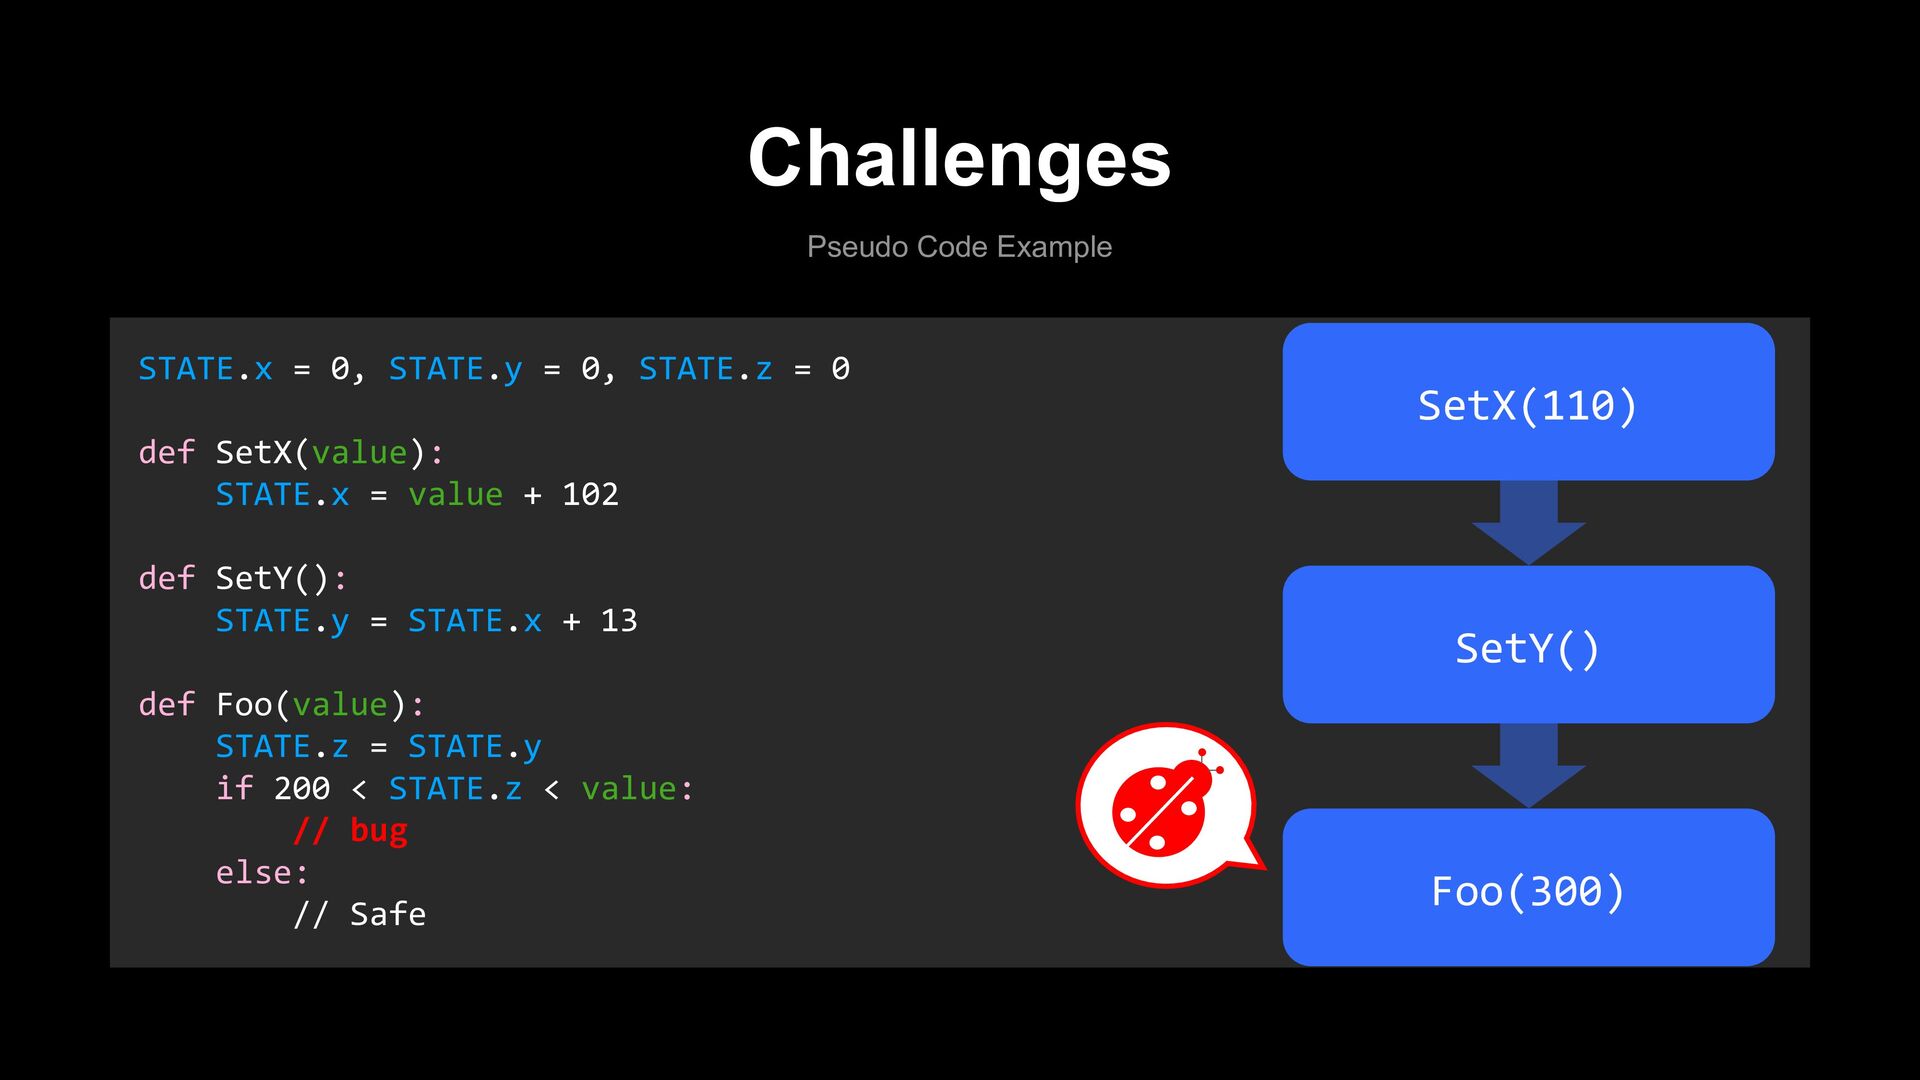
Challenges Pseudo Code Example STATE.x = 0, STATE.y = 0,
STATE.z = 0 def SetX(value): STATE.x = value + 102 def SetY(): STATE.y = STATE.x + 13 def Foo(value): STATE.z = STATE.y if 200 < STATE.z < value: // bug else: // Safe SetX(110) Foo(300) SetY() -
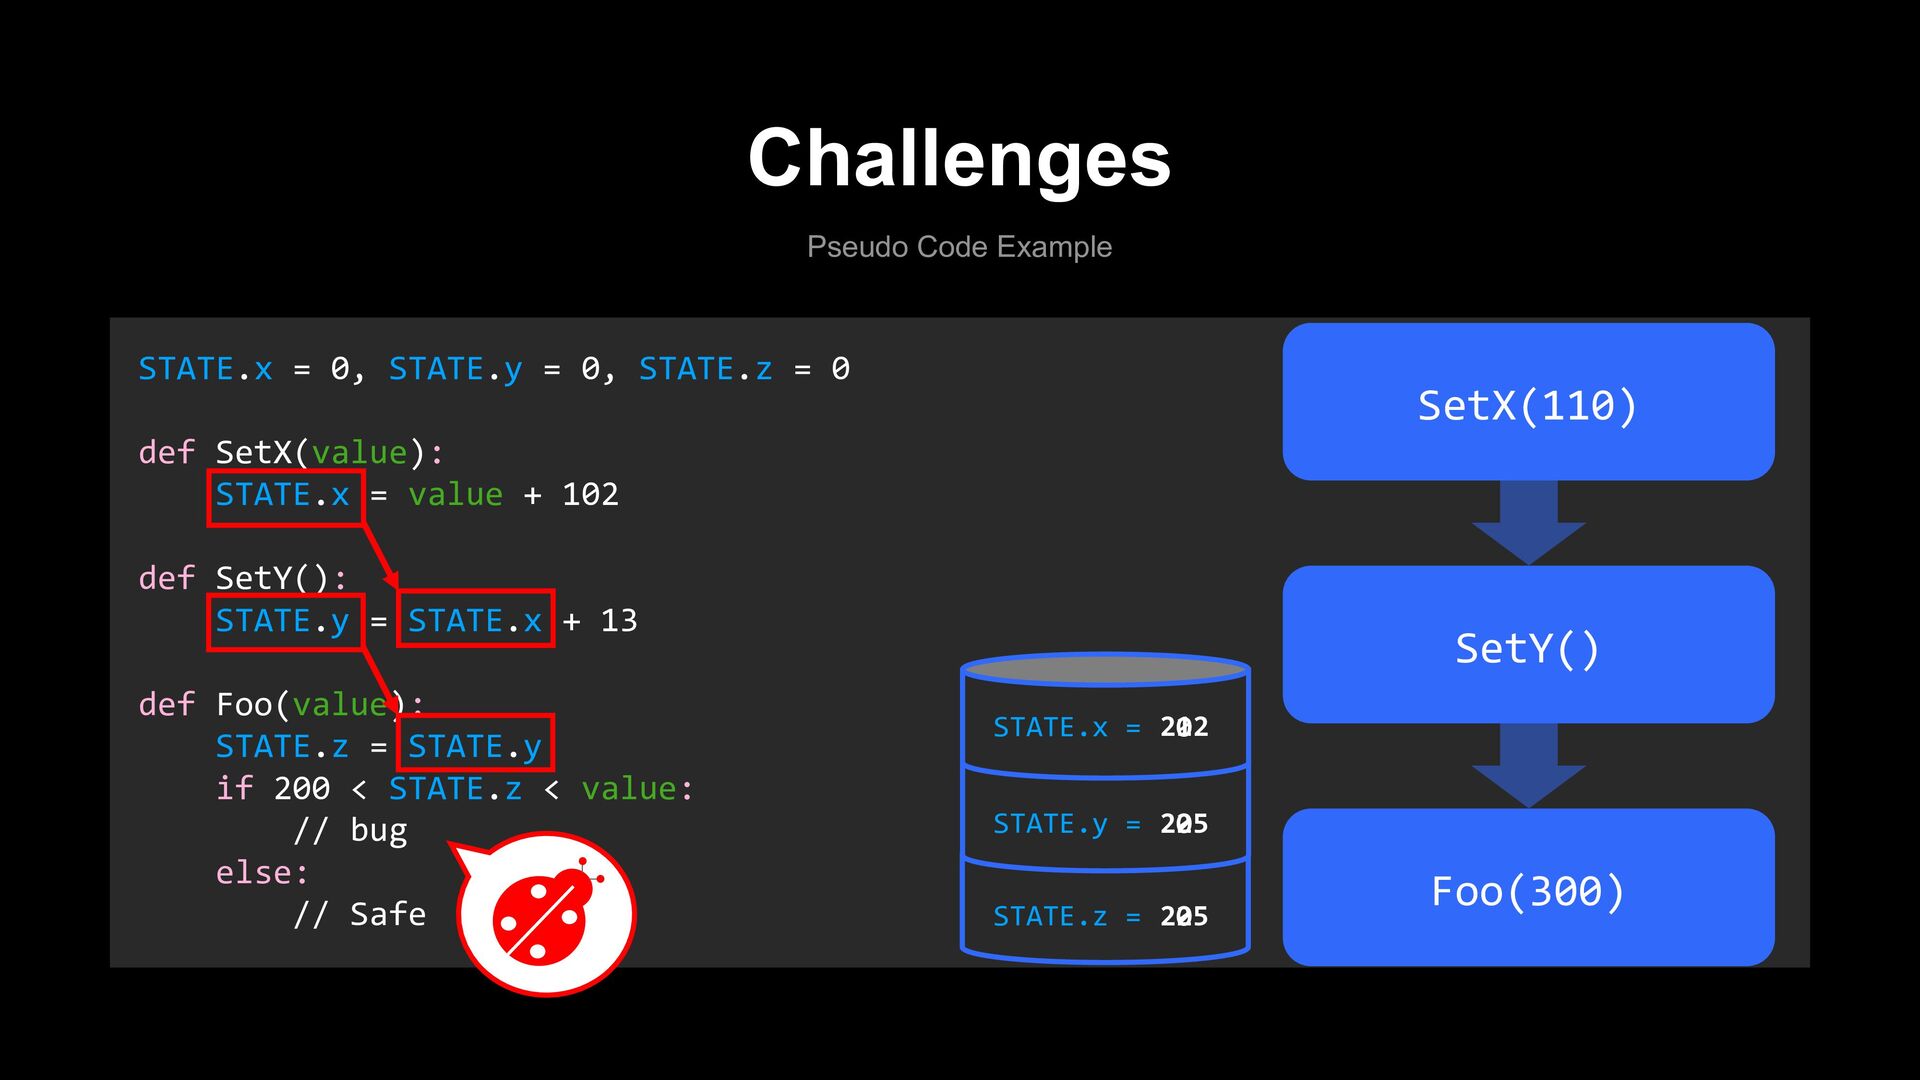
Challenges Pseudo Code Example STATE.x = 0, STATE.y = 0,
STATE.z = 0 def SetX(value): STATE.x = value + 102 def SetY(): STATE.y = STATE.x + 13 def Foo(value): STATE.z = STATE.y if 200 < STATE.z < value: // bug else: // Safe SetX(110) Foo(300) SetY() STATE.x = STATE.y = STATE.z = 0 0 0 212 225 225 -
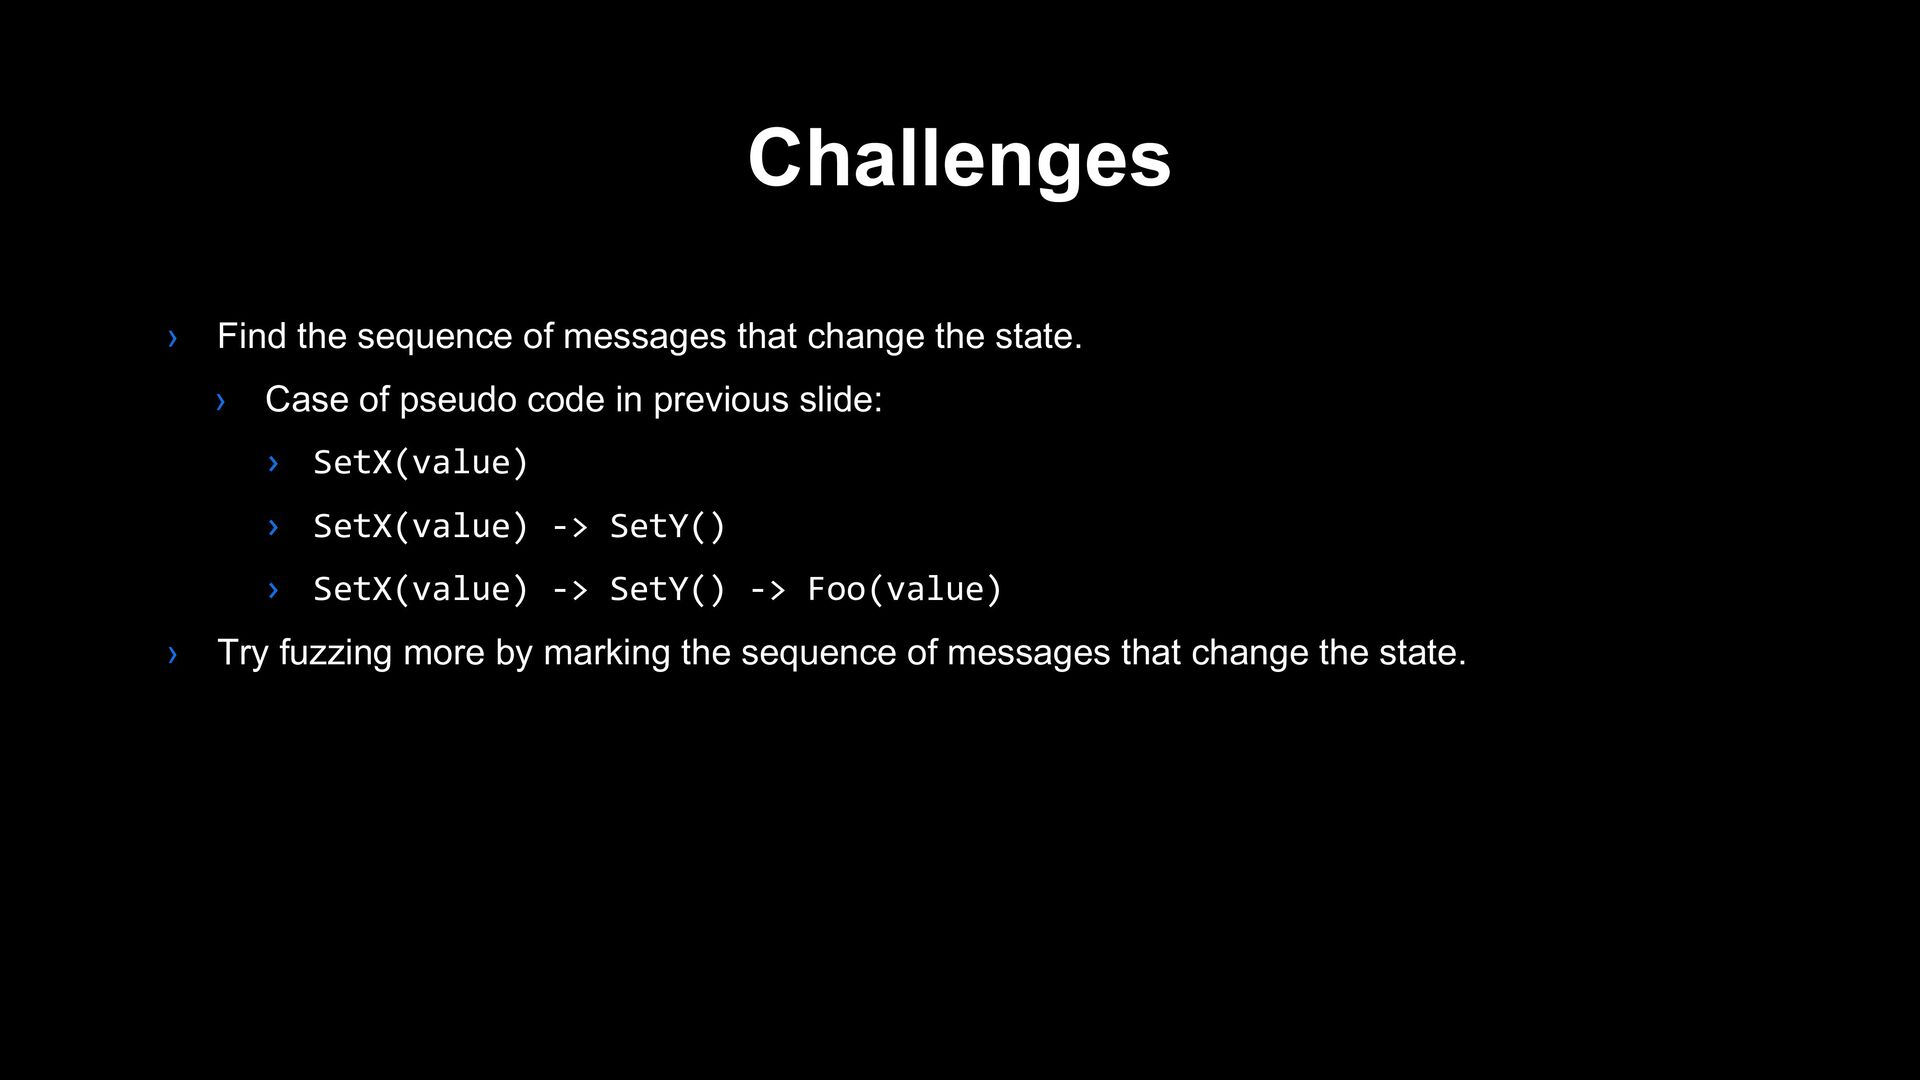
Challenges › Find the sequence of messages that change the
state. › Case of pseudo code in previous slide: › SetX(value) › SetX(value) -> SetY() › SetX(value) -> SetY() -> Foo(value) › Try fuzzing more by marking the sequence of messages that change the state. -
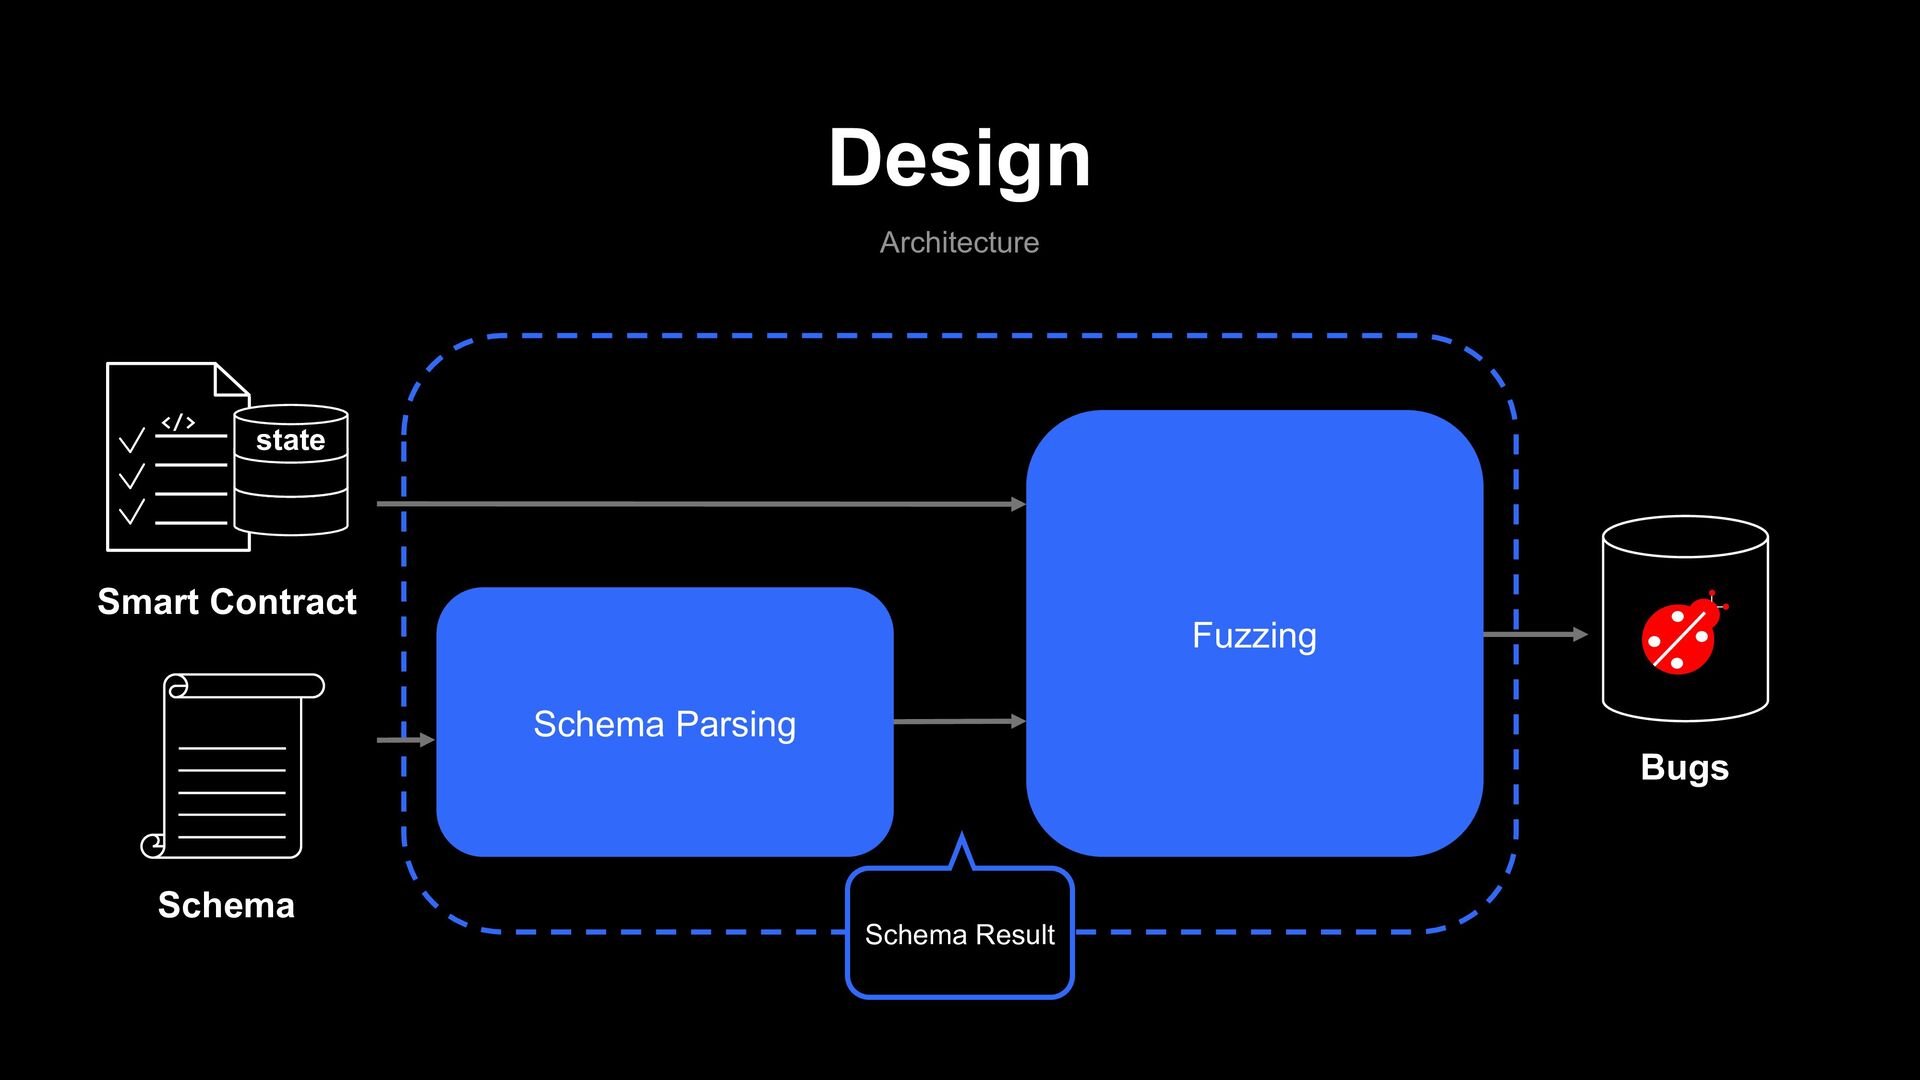
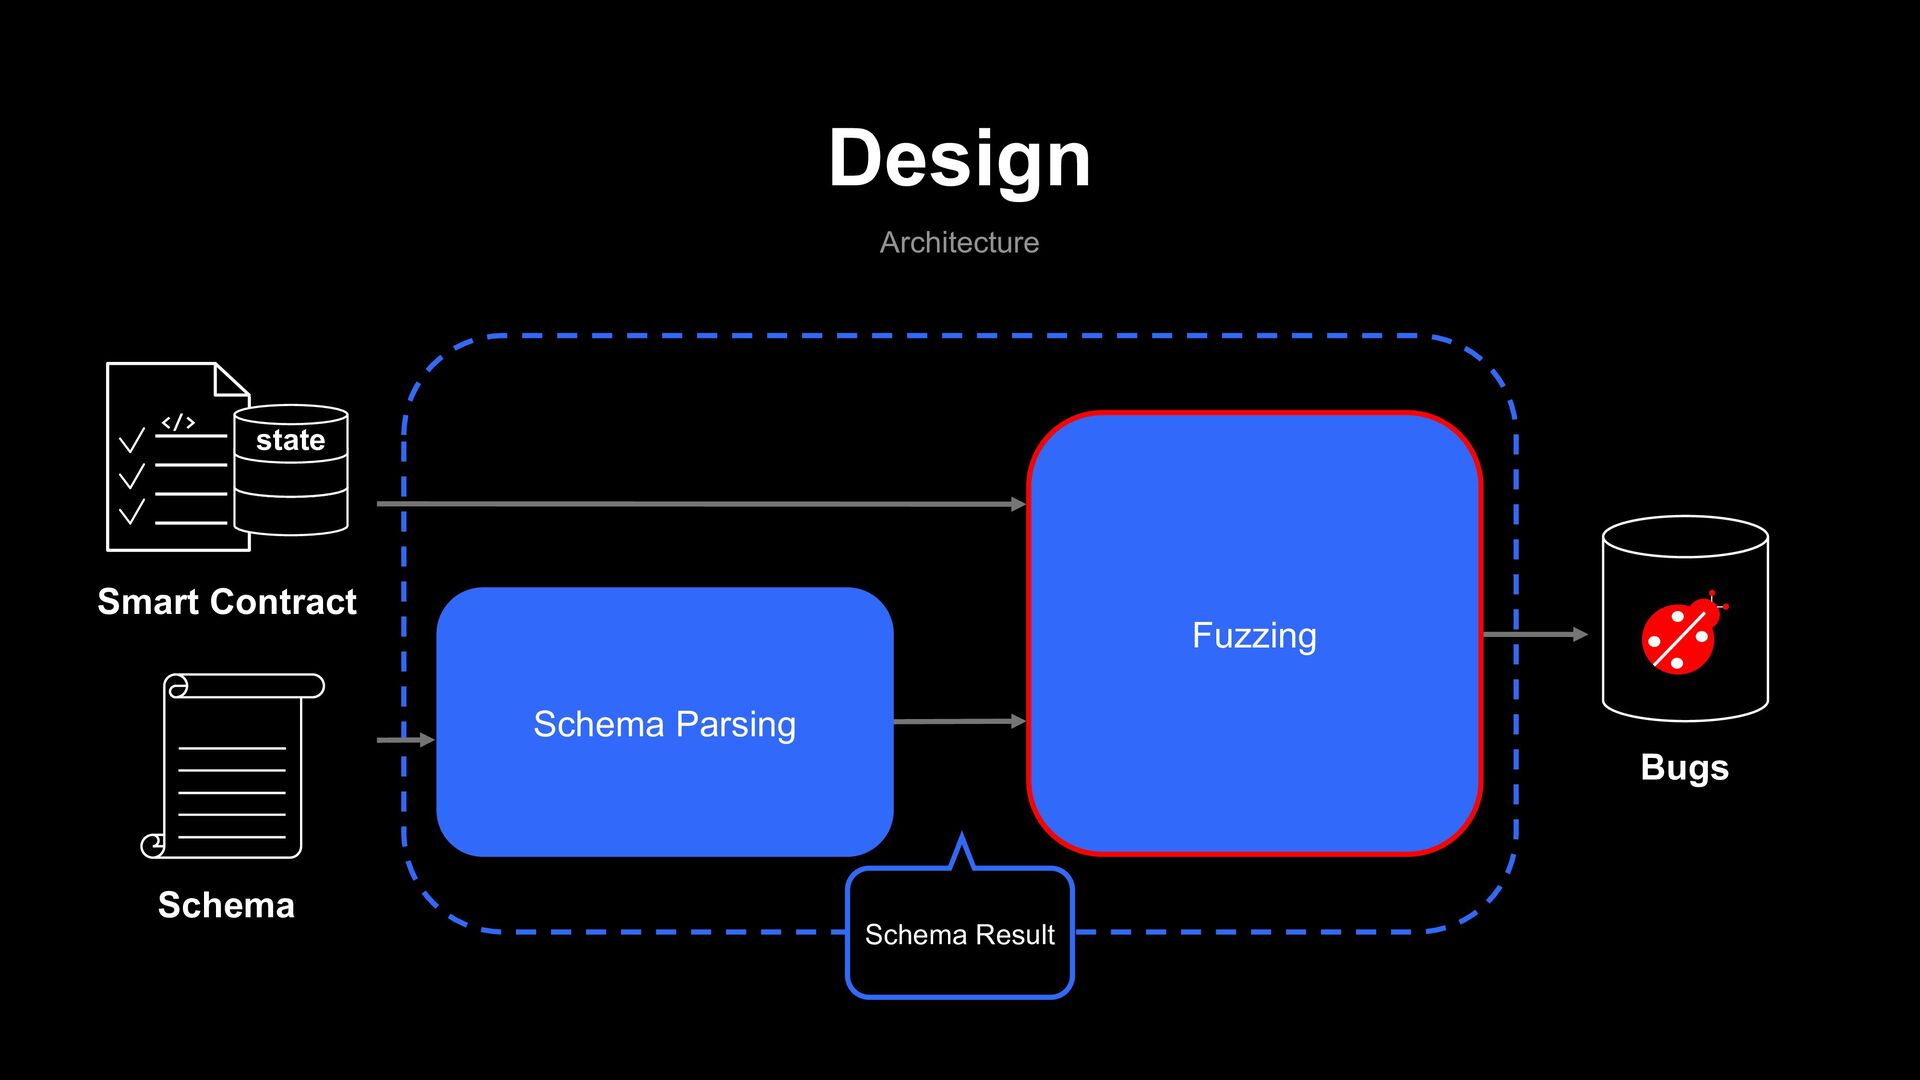
Design Schema Bugs Architecture </> state Smart Contract Schema Parsing
Fuzzing Schema Result -
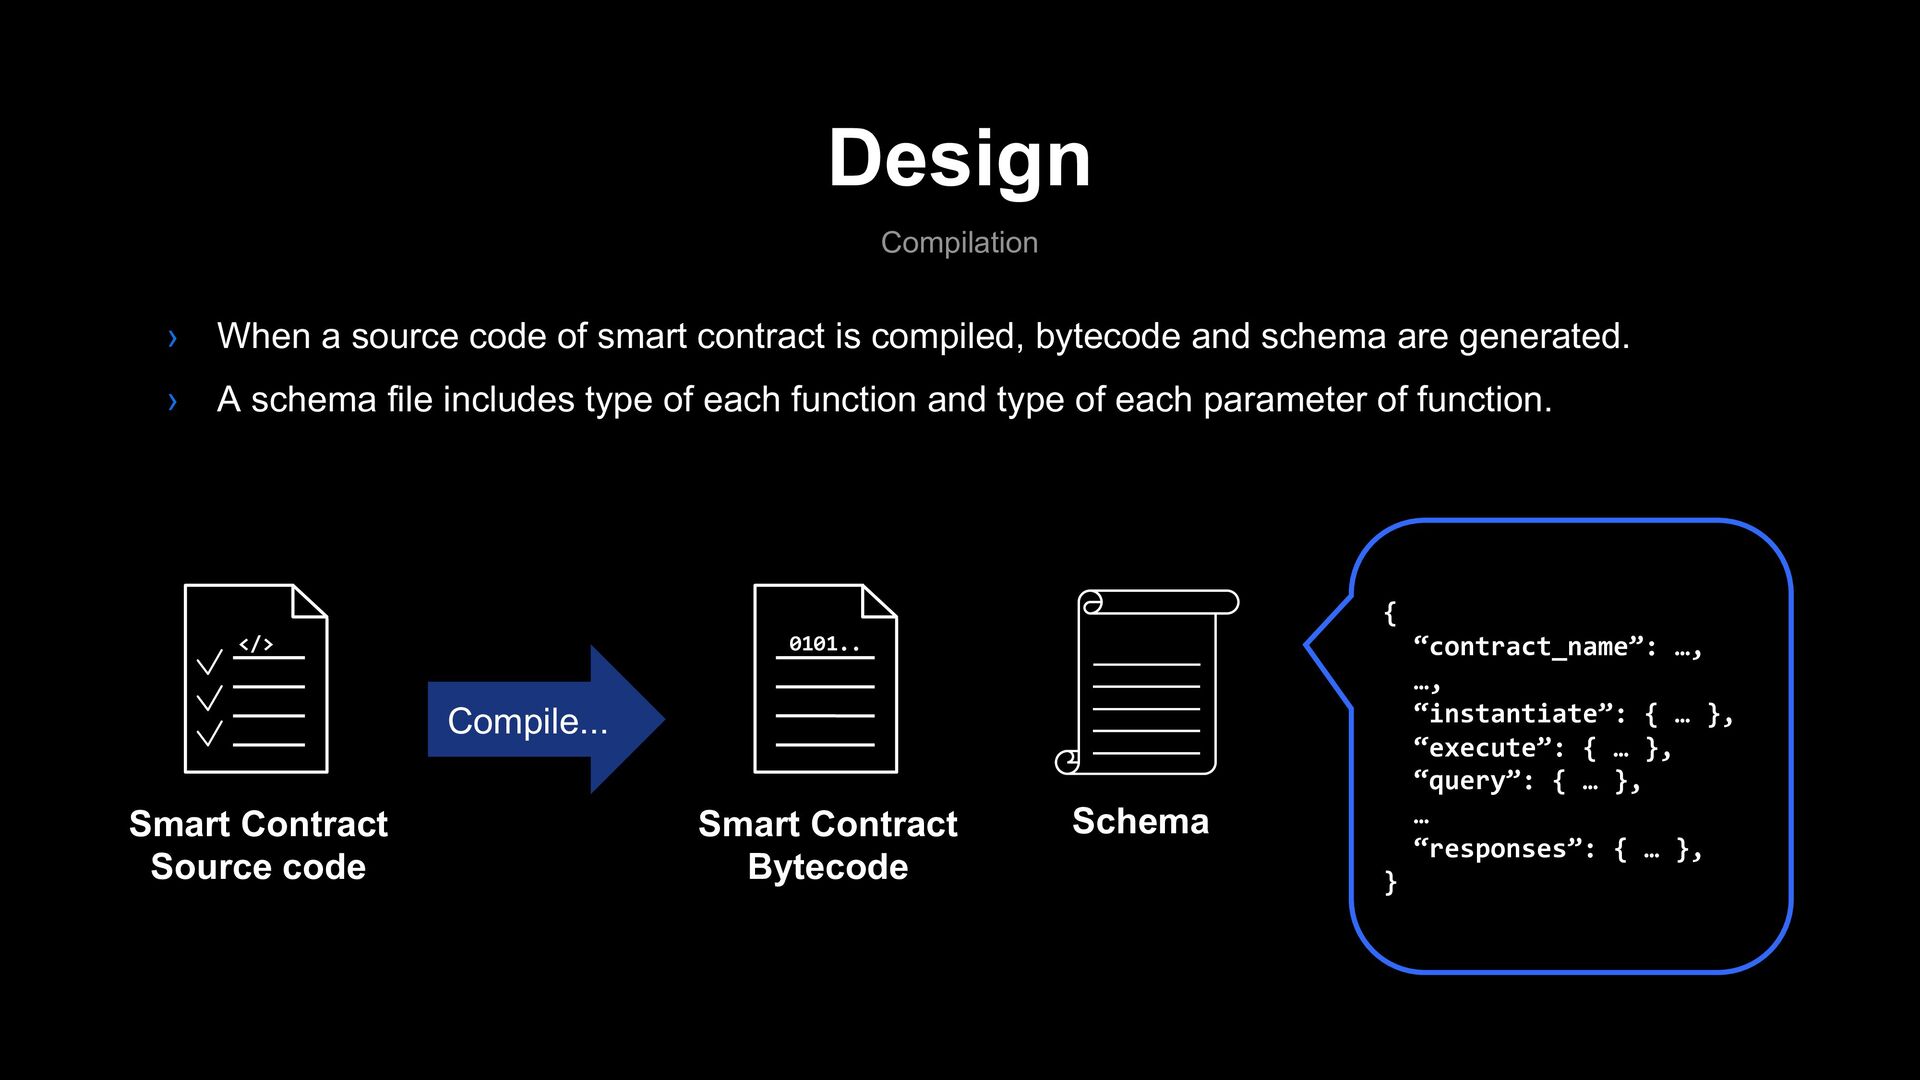
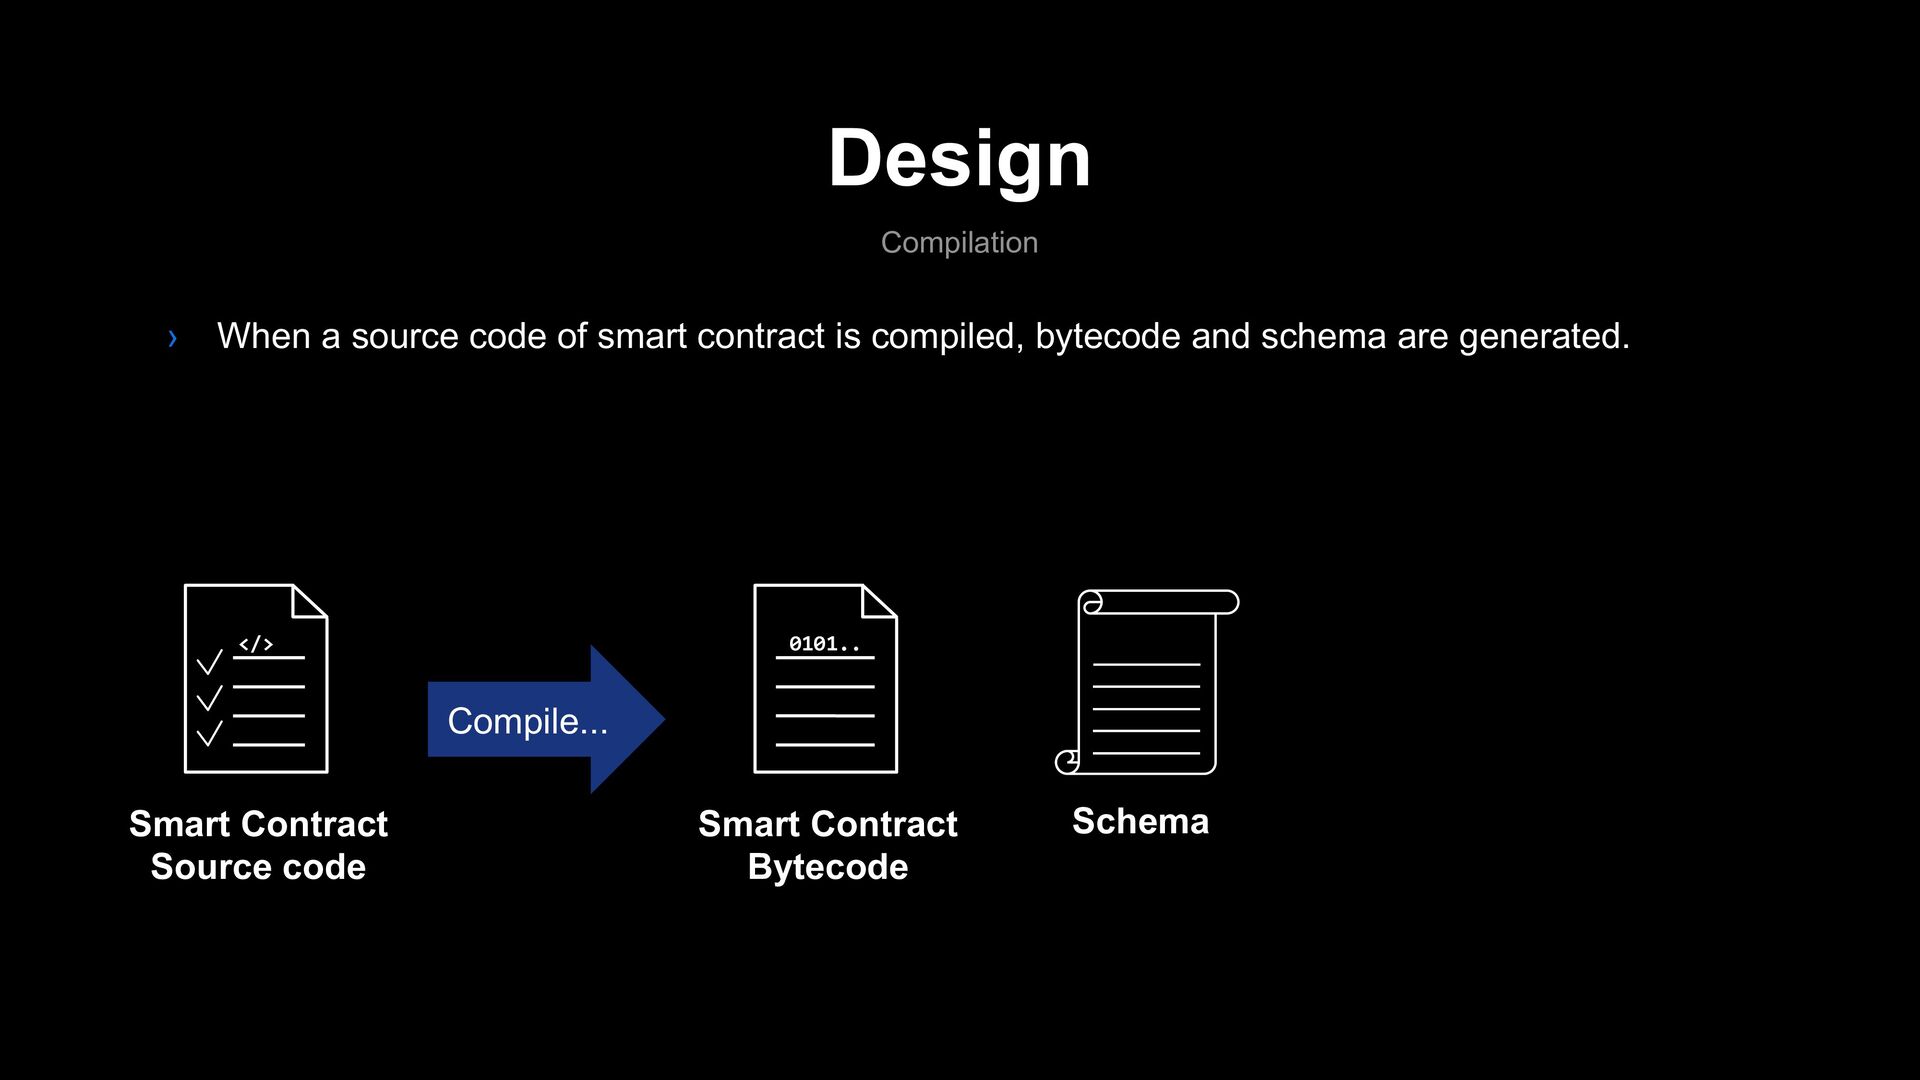
Design Compilation Schema </> Smart Contract Source code 0101.. Smart
Contract Bytecode › When a source code of smart contract is compiled, bytecode and schema are generated. Compile... -
Design Compilation Schema </> Smart Contract Source code { “contract_name”:
…, …, “instantiate”: { … }, “execute”: { … }, “query”: { … }, … “responses”: { … }, } 0101.. Smart Contract Bytecode › When a source code of smart contract is compiled, bytecode and schema are generated. › A schema file includes type of each function and type of each parameter of function. Compile... -
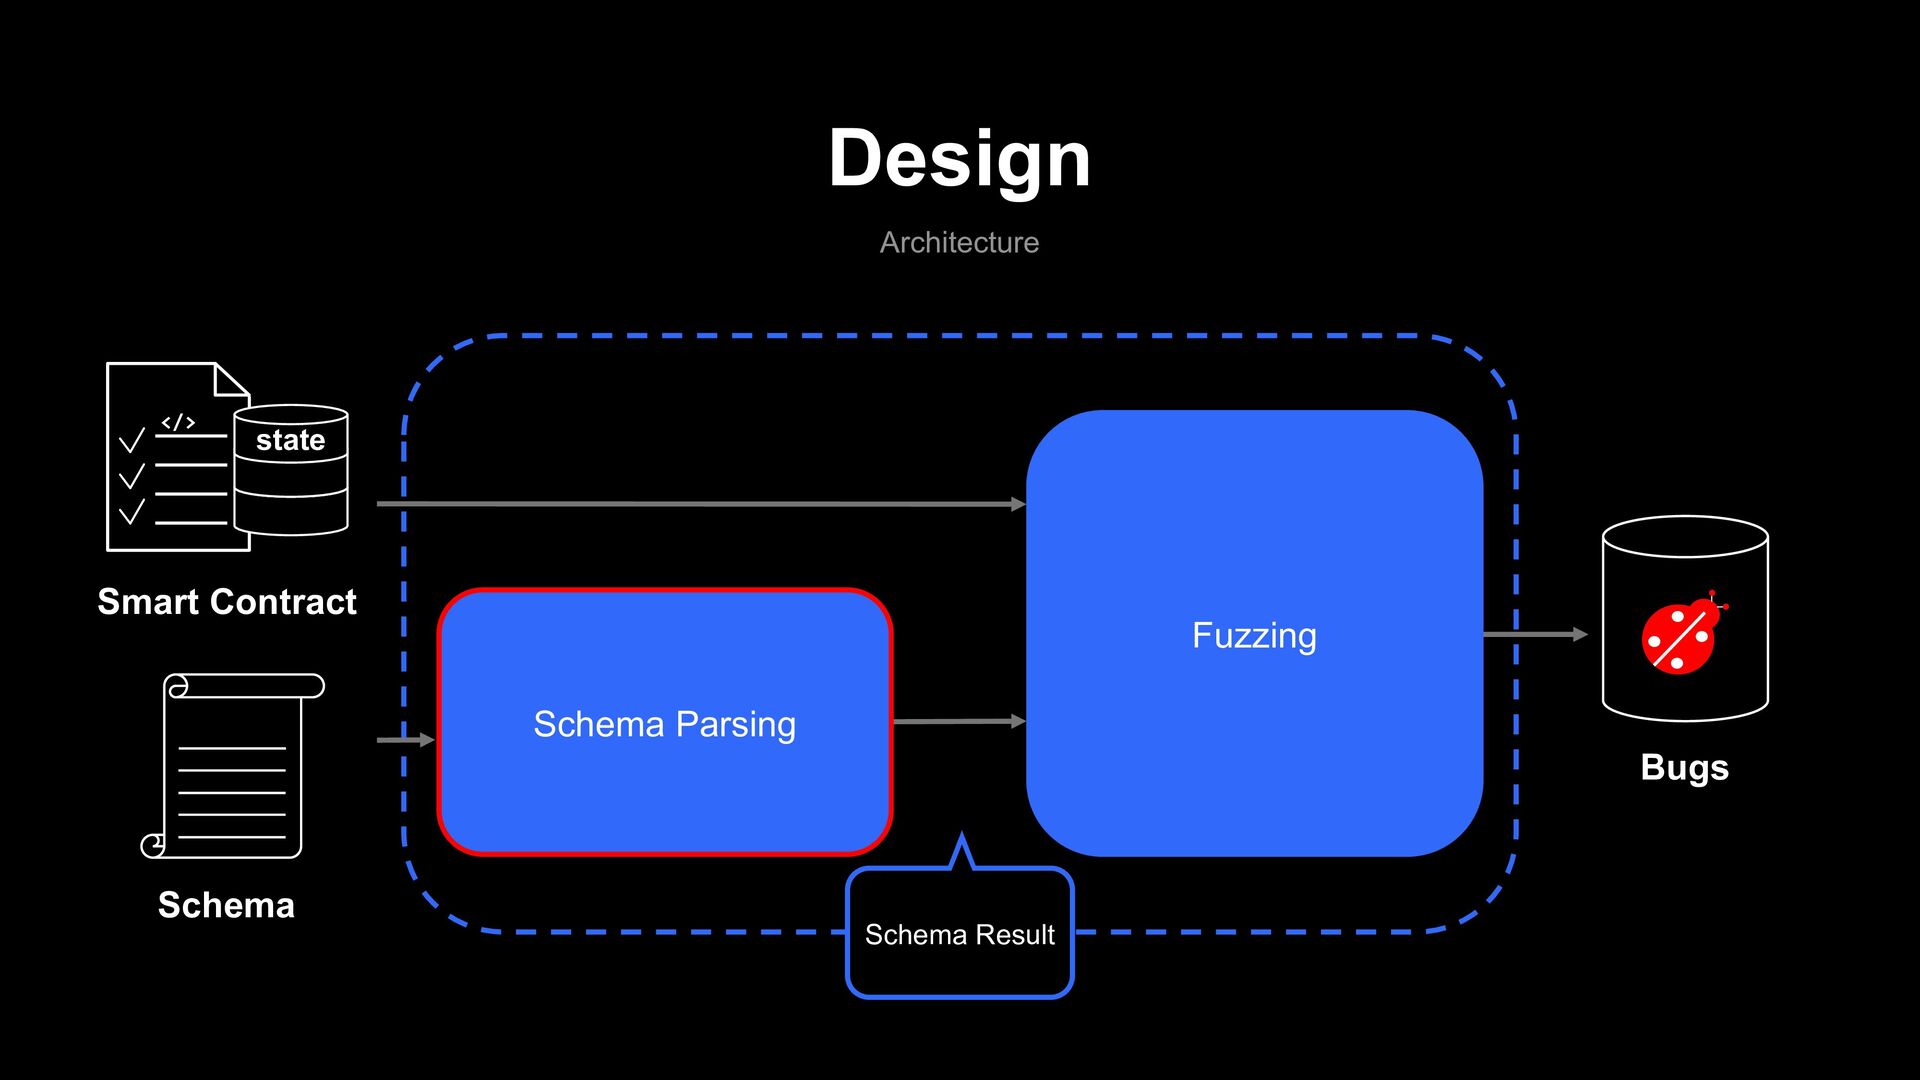
Design Schema Bugs Architecture </> state Smart Contract Schema Parsing
Fuzzing Schema Result -
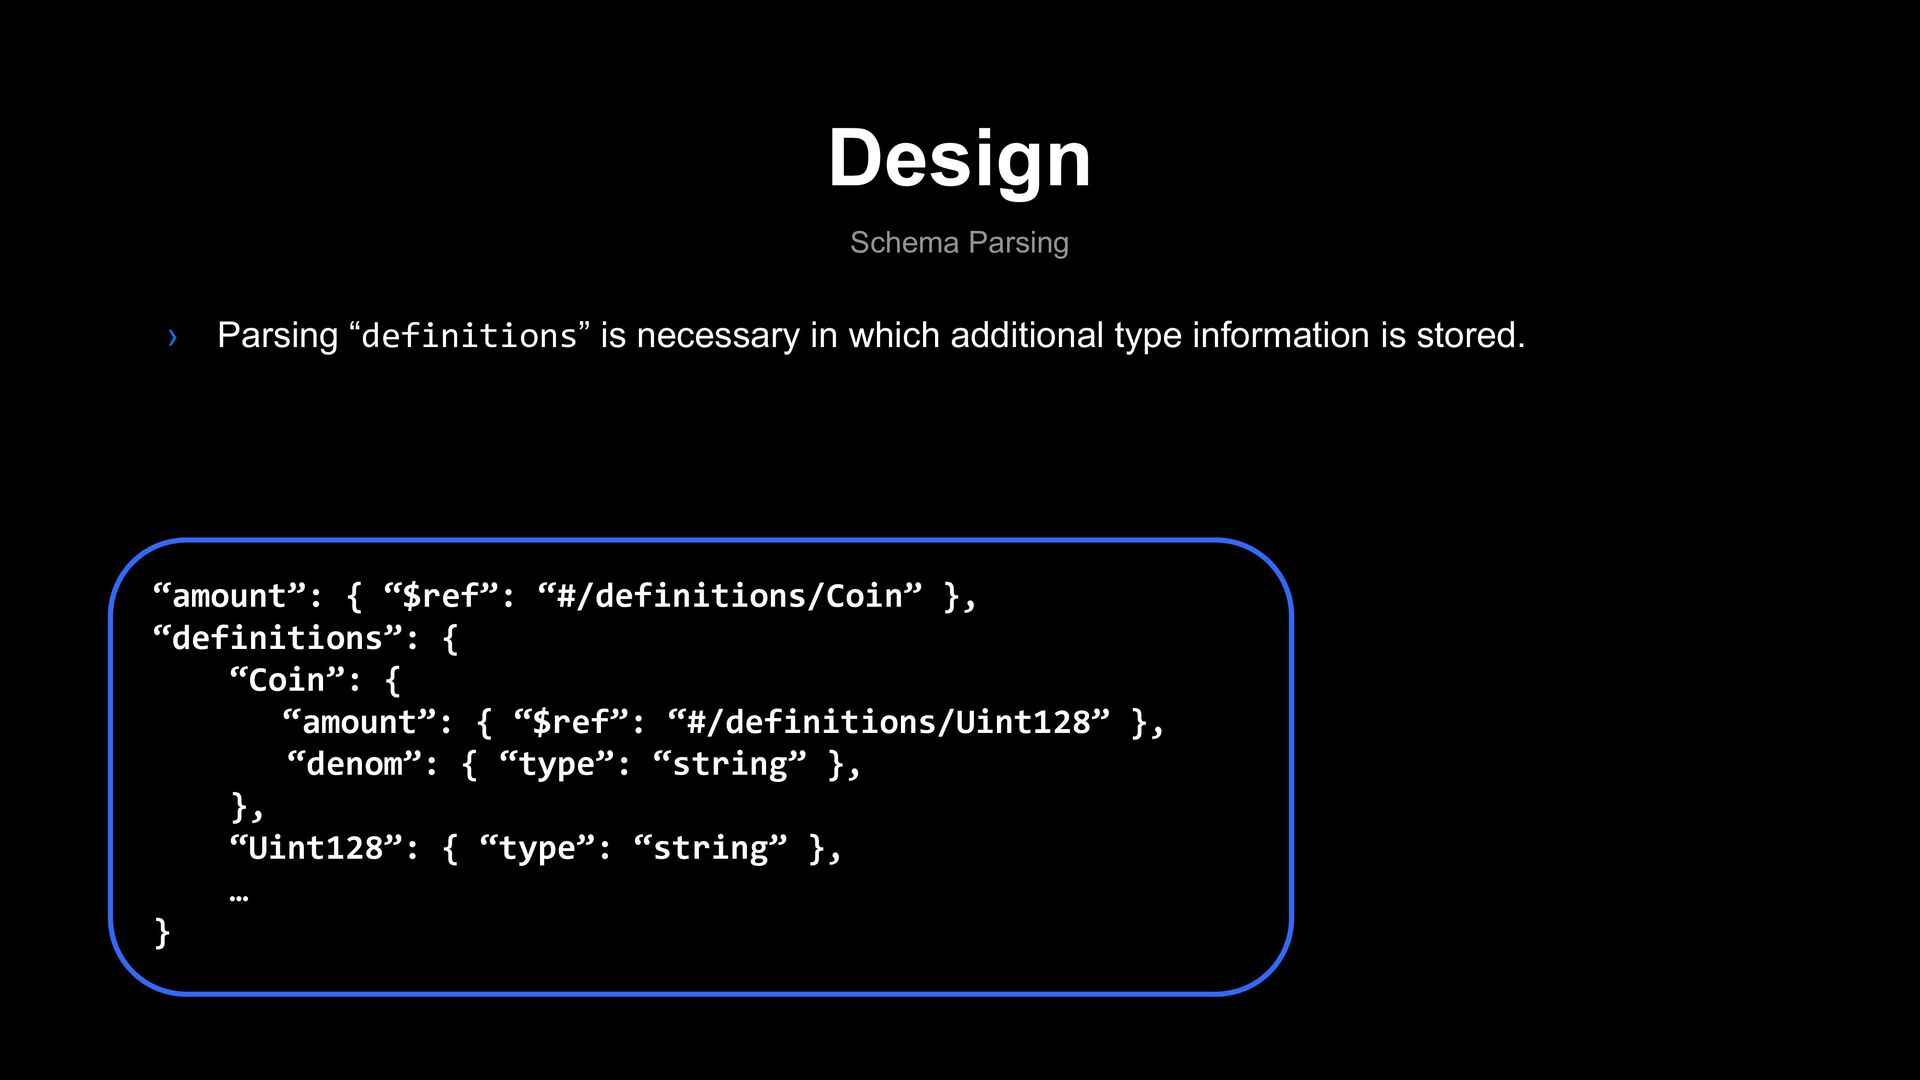
Design Schema Parsing › Parsing “definitions” is necessary in which
additional type information is stored. “amount”: { “$ref”: “#/definitions/Coin” }, “definitions”: { “Coin”: { “amount”: { “$ref”: “#/definitions/Uint128” }, “denom”: { “type”: “string” }, }, “Uint128”: { “type”: “string” }, … } -
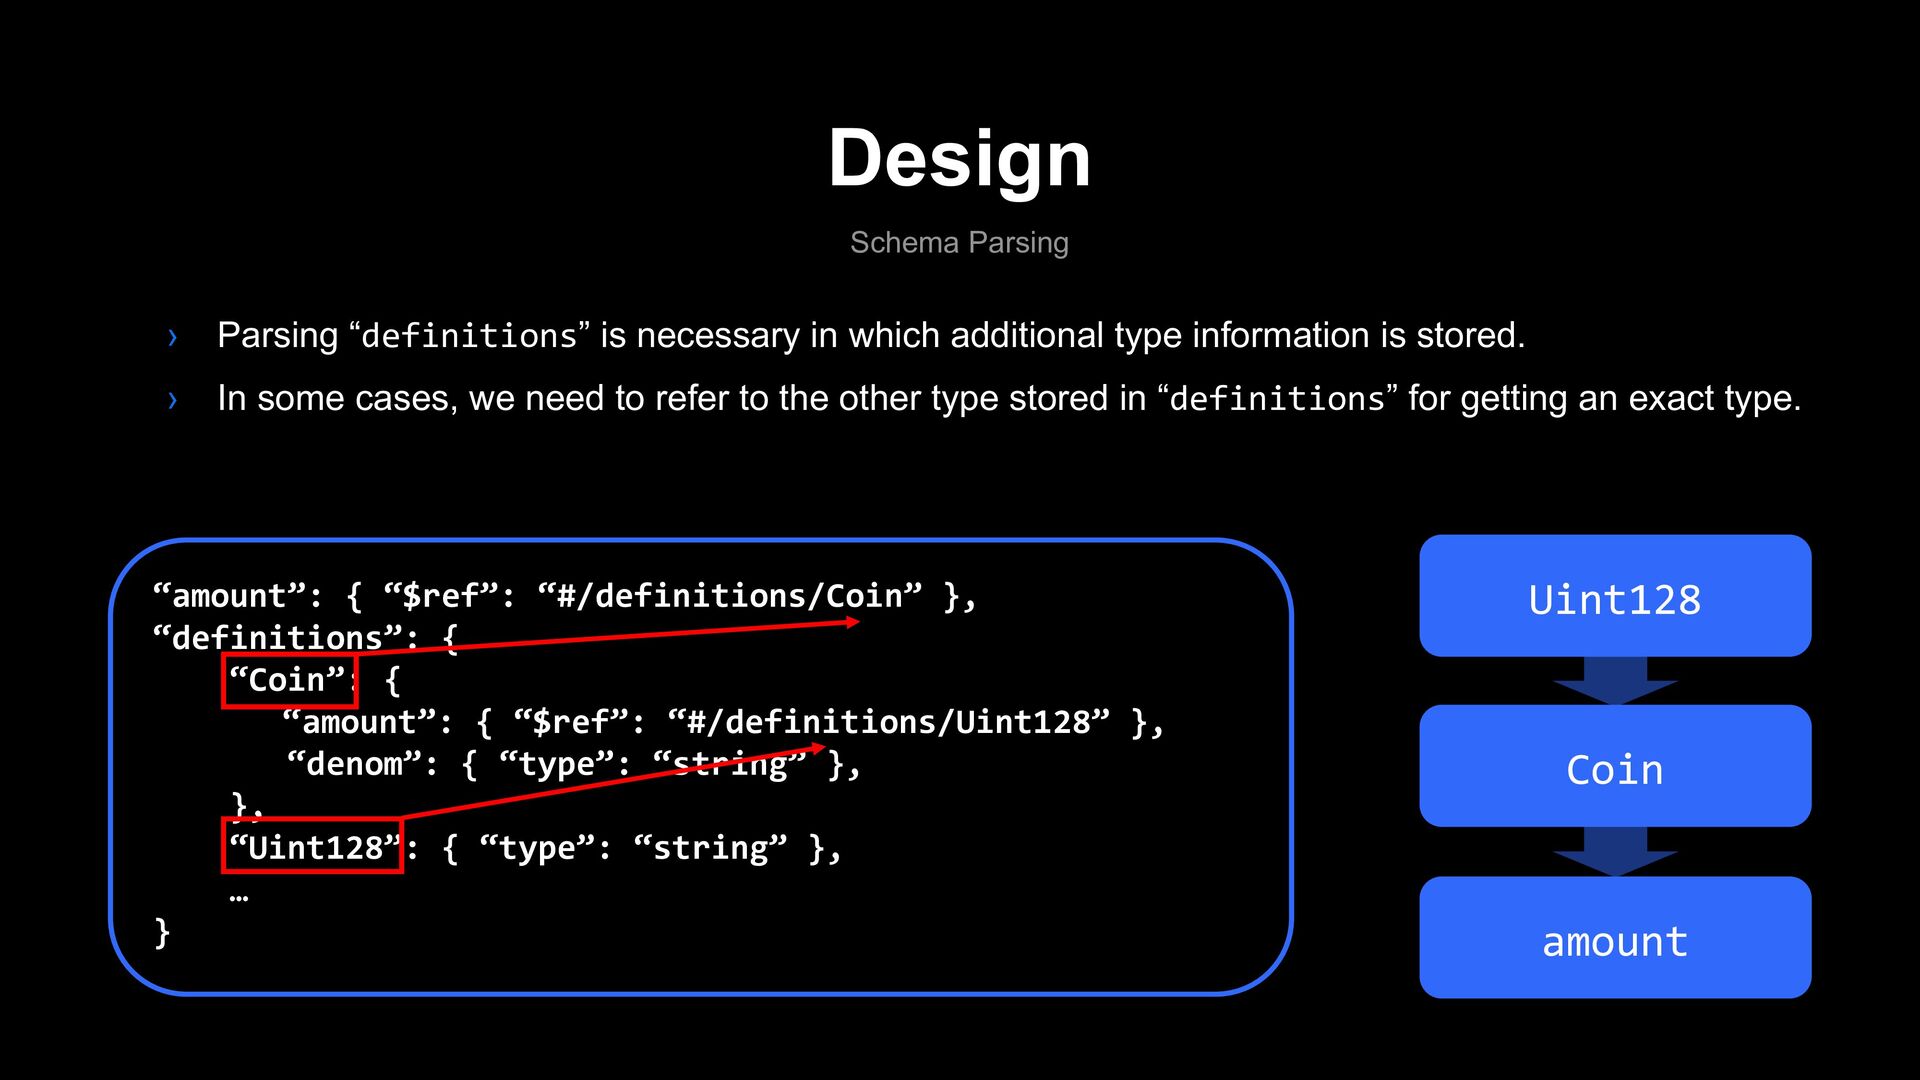
Design Schema Parsing › Parsing “definitions” is necessary in which
additional type information is stored. › In some cases, we need to refer to the other type stored in “definitions” for getting an exact type. Uint128 Coin amount “amount”: { “$ref”: “#/definitions/Coin” }, “definitions”: { “Coin”: { “amount”: { “$ref”: “#/definitions/Uint128” }, “denom”: { “type”: “string” }, }, “Uint128”: { “type”: “string” }, … } -
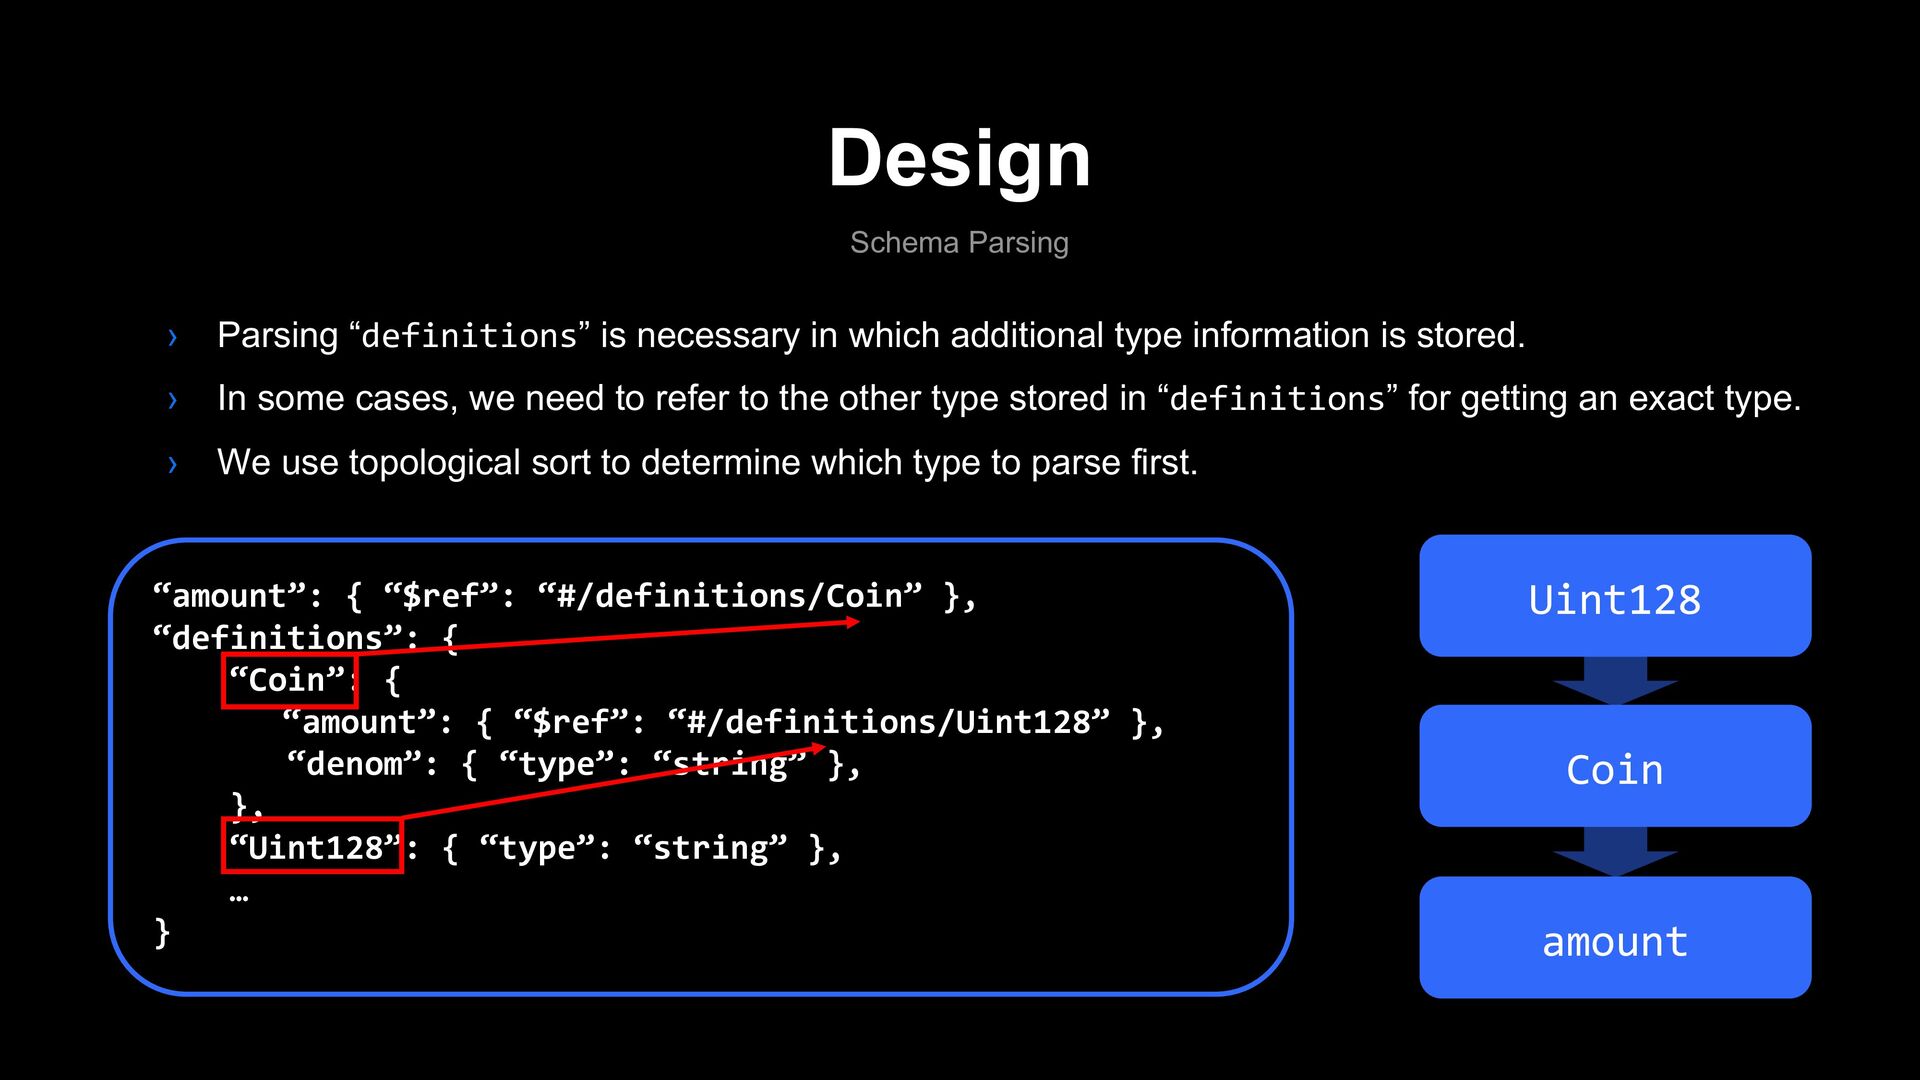
Design Schema Parsing › Parsing “definitions” is necessary in which
additional type information is stored. › In some cases, we need to refer to the other type stored in “definitions” for getting an exact type. › We use topological sort to determine which type to parse first. Uint128 Coin amount “amount”: { “$ref”: “#/definitions/Coin” }, “definitions”: { “Coin”: { “amount”: { “$ref”: “#/definitions/Uint128” }, “denom”: { “type”: “string” }, }, “Uint128”: { “type”: “string” }, … } -
Design Schema Bugs Architecture </> state Smart Contract Schema Parsing
Fuzzing Schema Result -
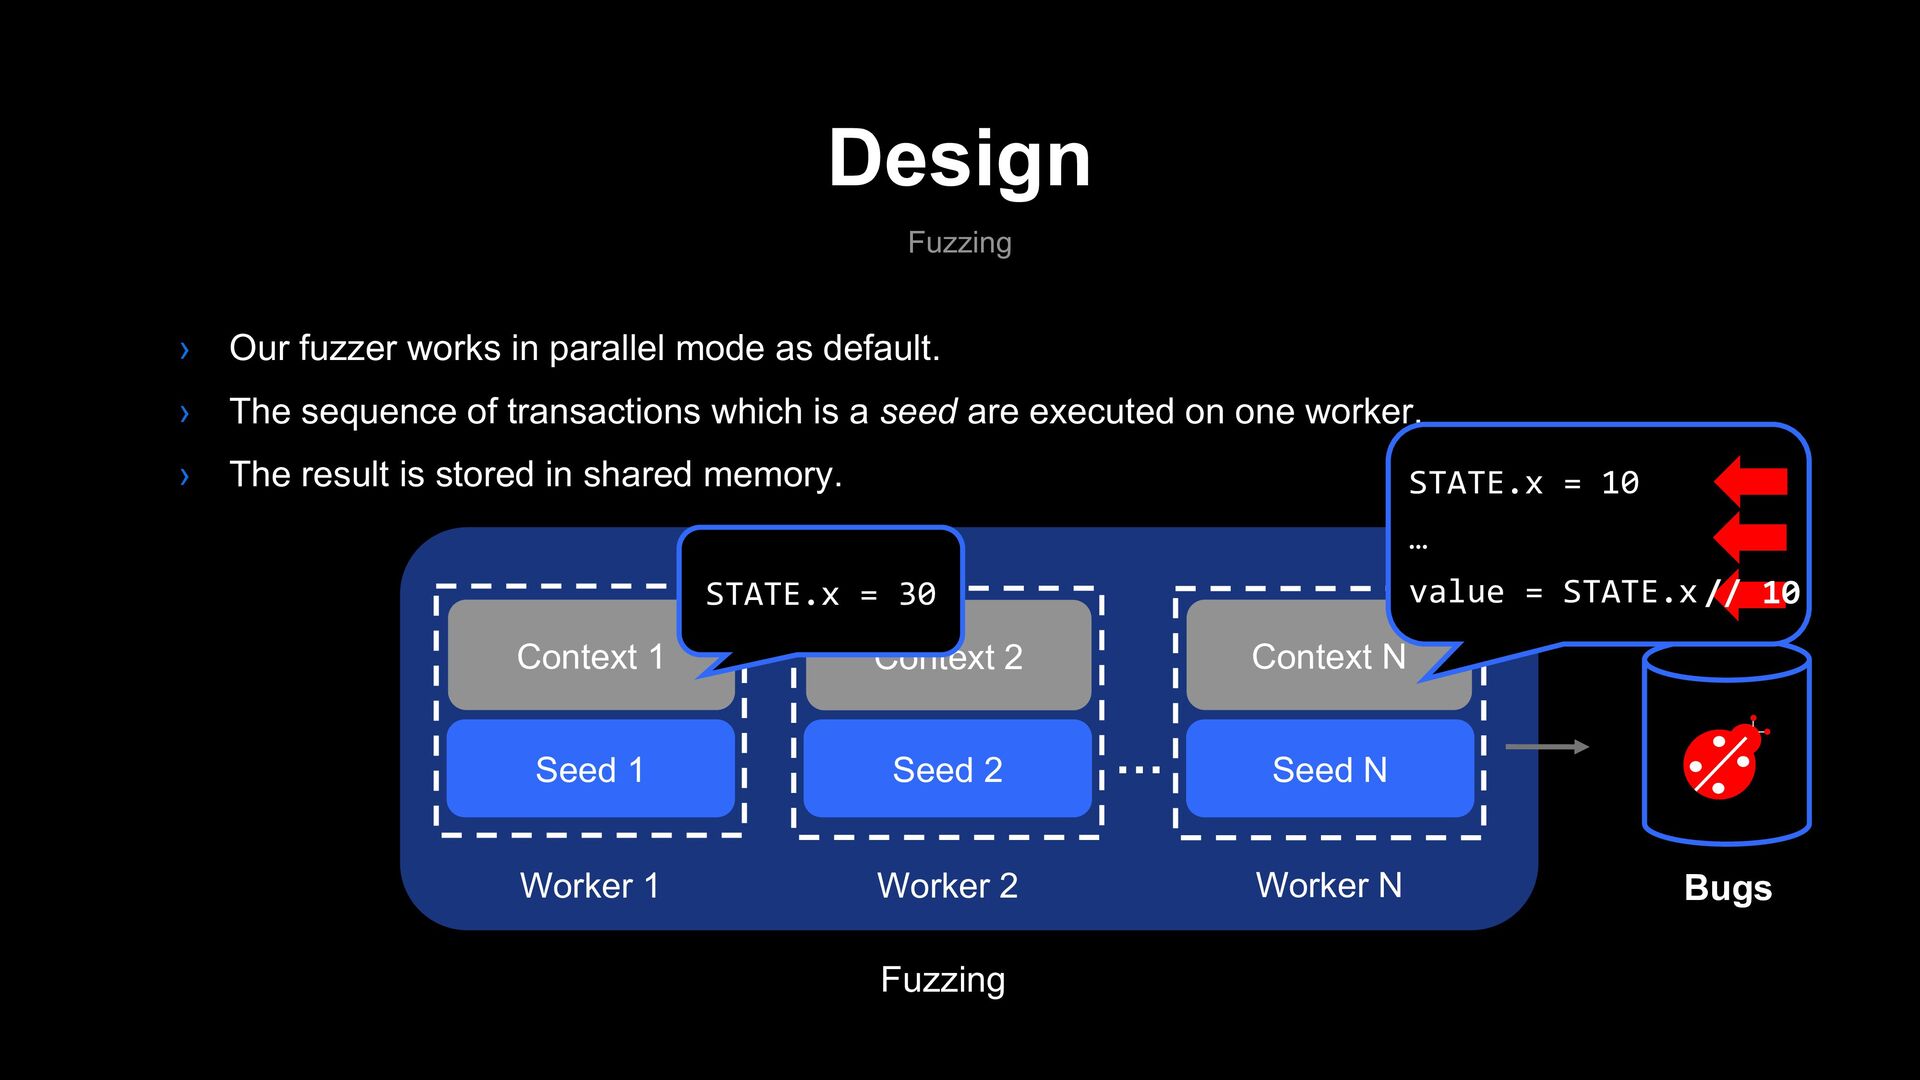
Design Fuzzing Fuzzing Seed 1 Bugs … Seed 2 Seed
N Worker 1 Worker 2 Worker N Context 1 Context 2 Context N › Our fuzzer works in parallel mode as default. › The sequence of transactions which is a seed are executed on one worker. › The result is stored in shared memory. STATE.x = 30 STATE.x = 10 … value = STATE.x // 10 -
Design Fuzzing › For discovering the flow of persistent state
variable indirectly, we send two query messages per transaction: One is before the transaction and the other is after the transaction. › We can find out which persistent state is updated in the transaction. -
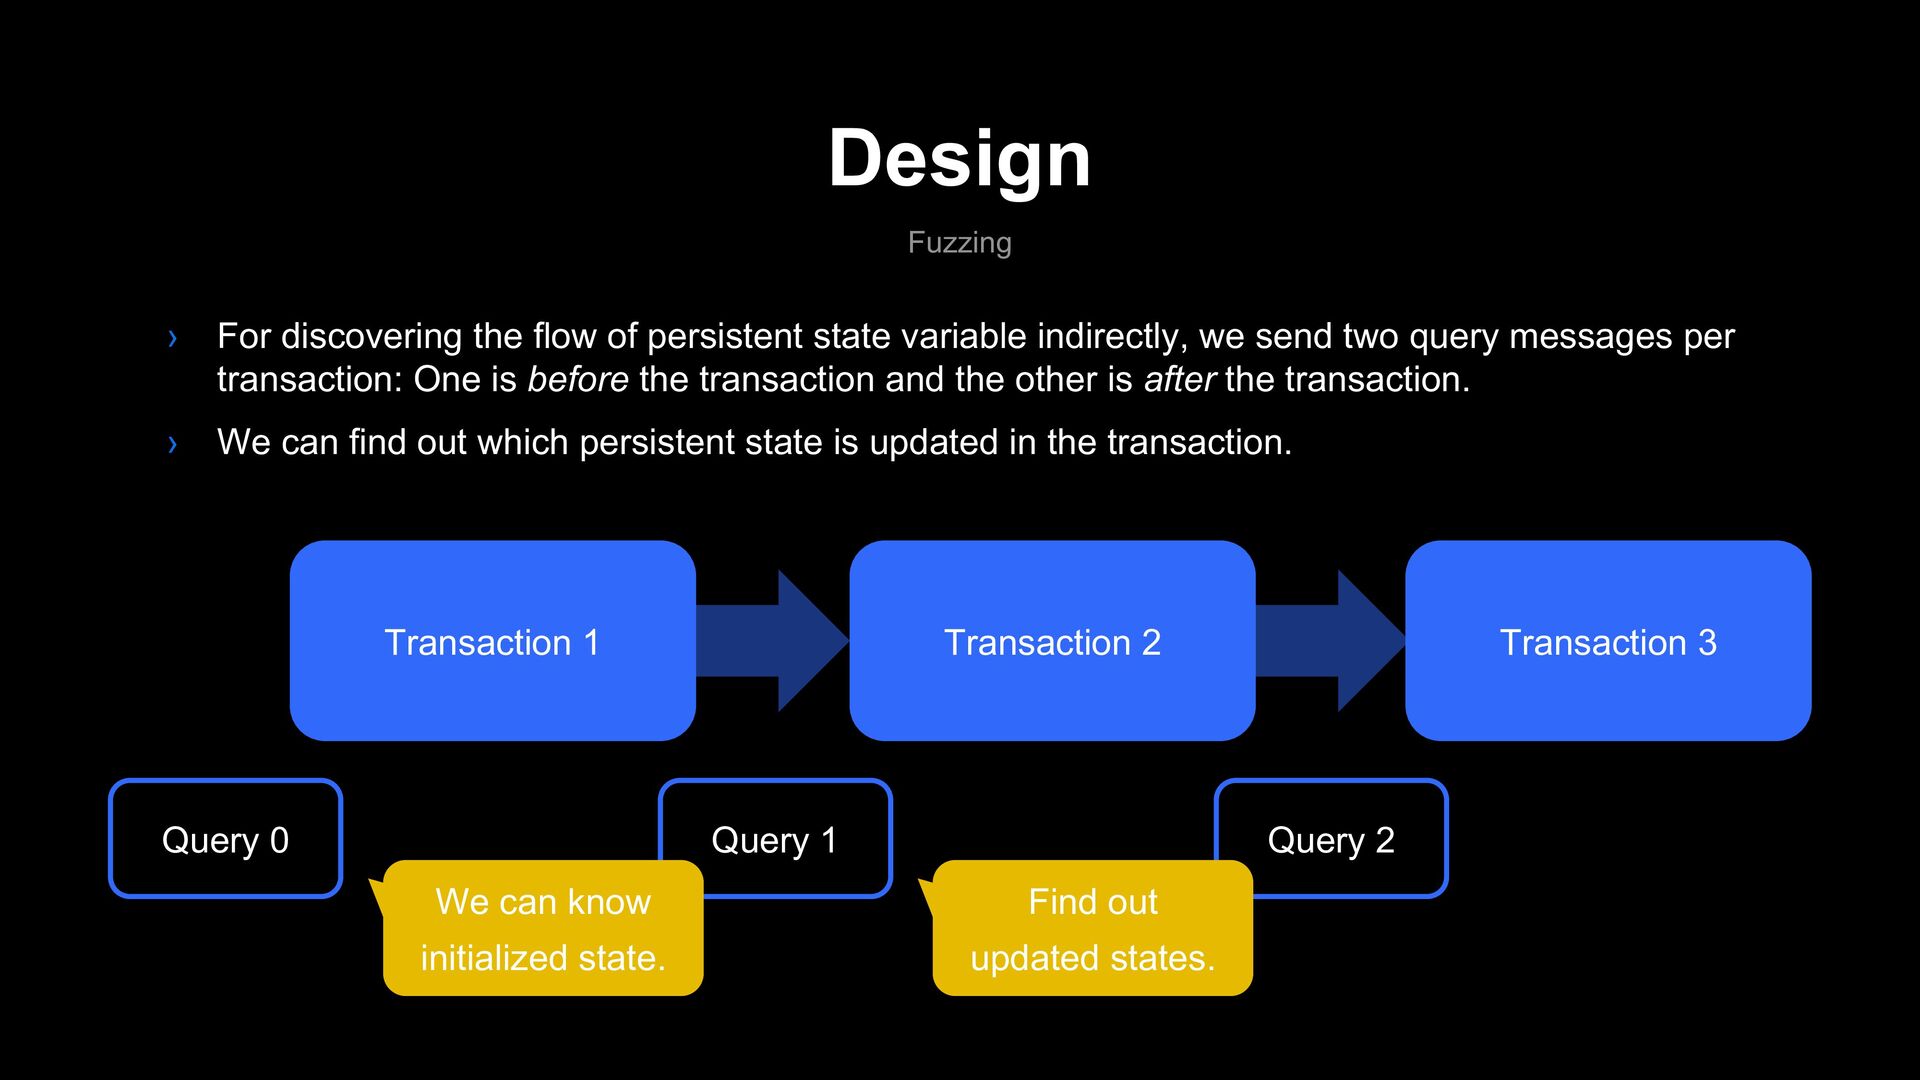
Design Fuzzing › For discovering the flow of persistent state
variable indirectly, we send two query messages per transaction: One is before the transaction and the other is after the transaction. › We can find out which persistent state is updated in the transaction. Transaction 1 Transaction 3 Transaction 2 Query 0 Query 1 Query 2 We can know initialized state. Find out updated states. -
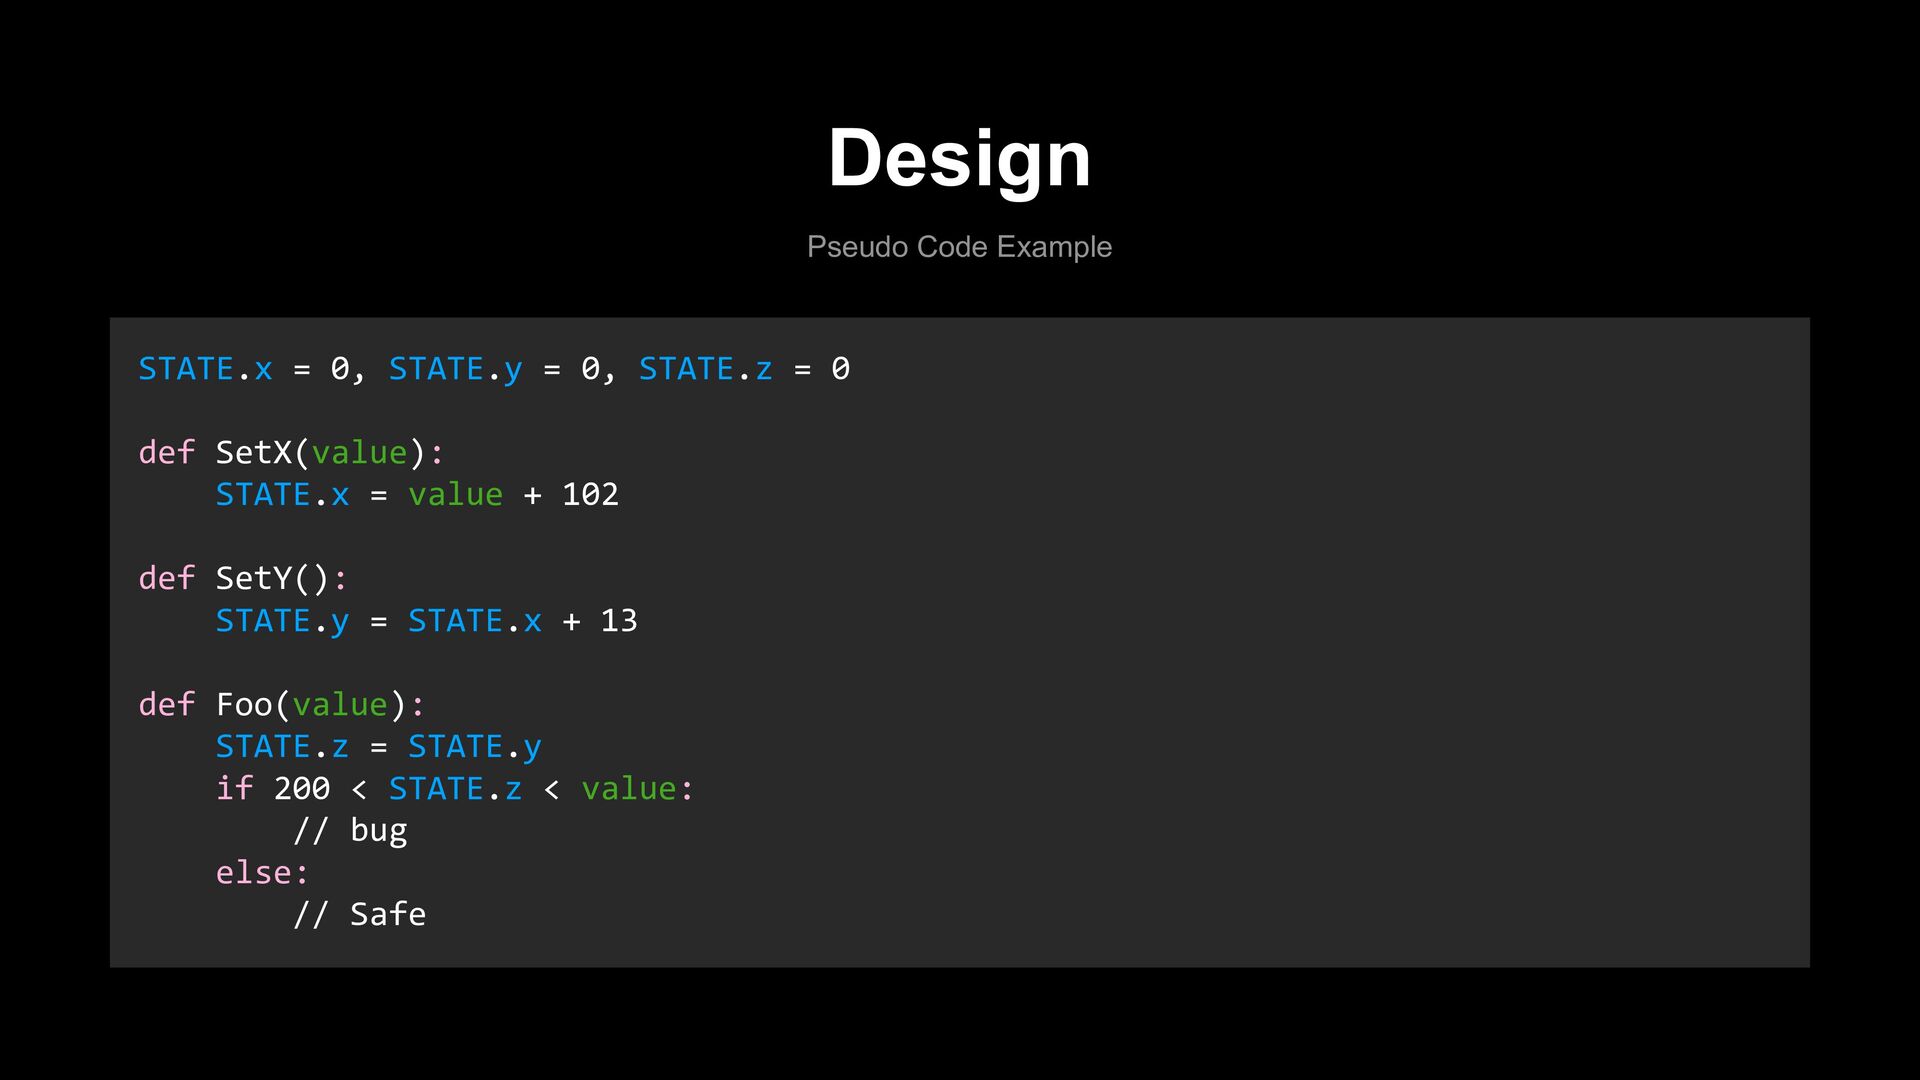
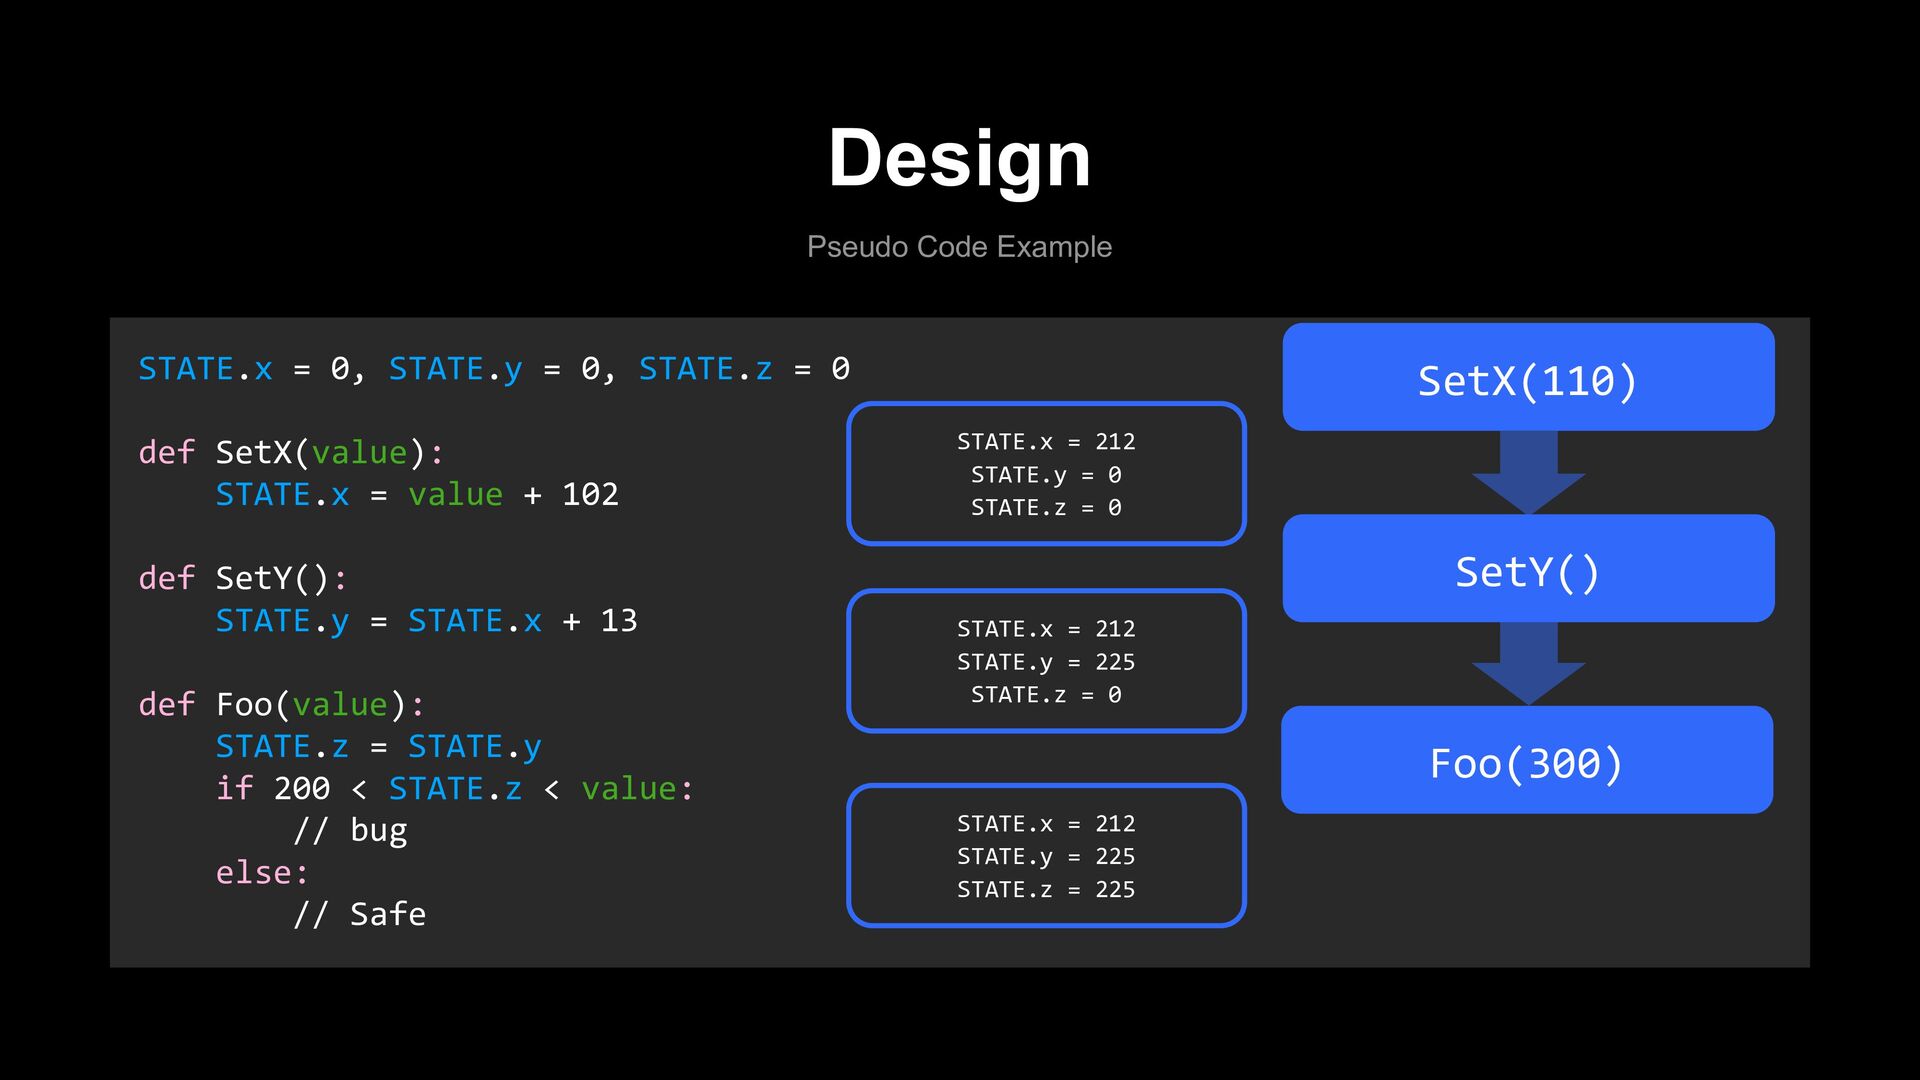
Design Pseudo Code Example STATE.x = 0, STATE.y = 0,
STATE.z = 0 def SetX(value): STATE.x = value + 102 def SetY(): STATE.y = STATE.x + 13 def Foo(value): STATE.z = STATE.y if 200 < STATE.z < value: // bug else: // Safe -
Design Pseudo Code Example STATE.x = 0, STATE.y = 0,
STATE.z = 0 def SetX(value): STATE.x = value + 102 def SetY(): STATE.y = STATE.x + 13 def Foo(value): STATE.z = STATE.y if 200 < STATE.z < value: // bug else: // Safe SetX(110) Foo(300) SetY() STATE.x = 212 STATE.y = 0 STATE.z = 0 STATE.x = 212 STATE.y = 225 STATE.z = 0 STATE.x = 212 STATE.y = 225 STATE.z = 225 -
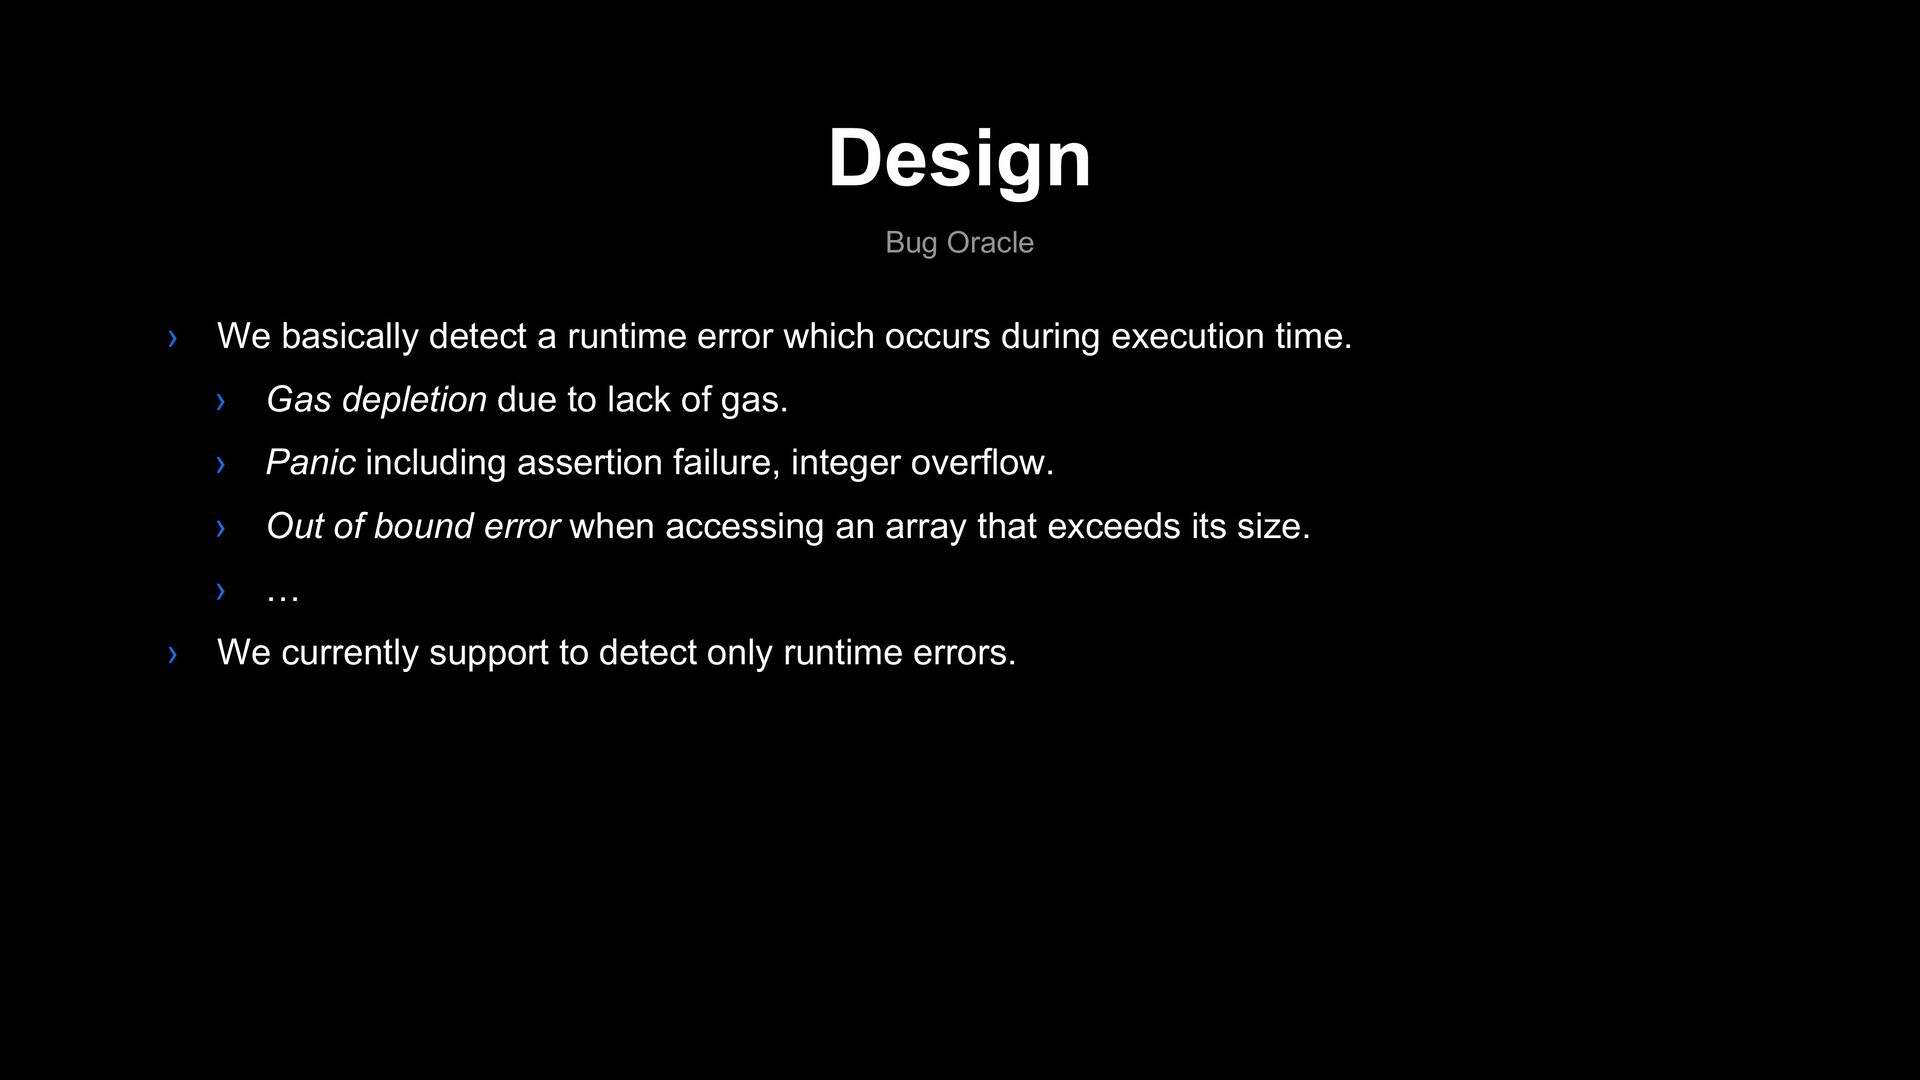
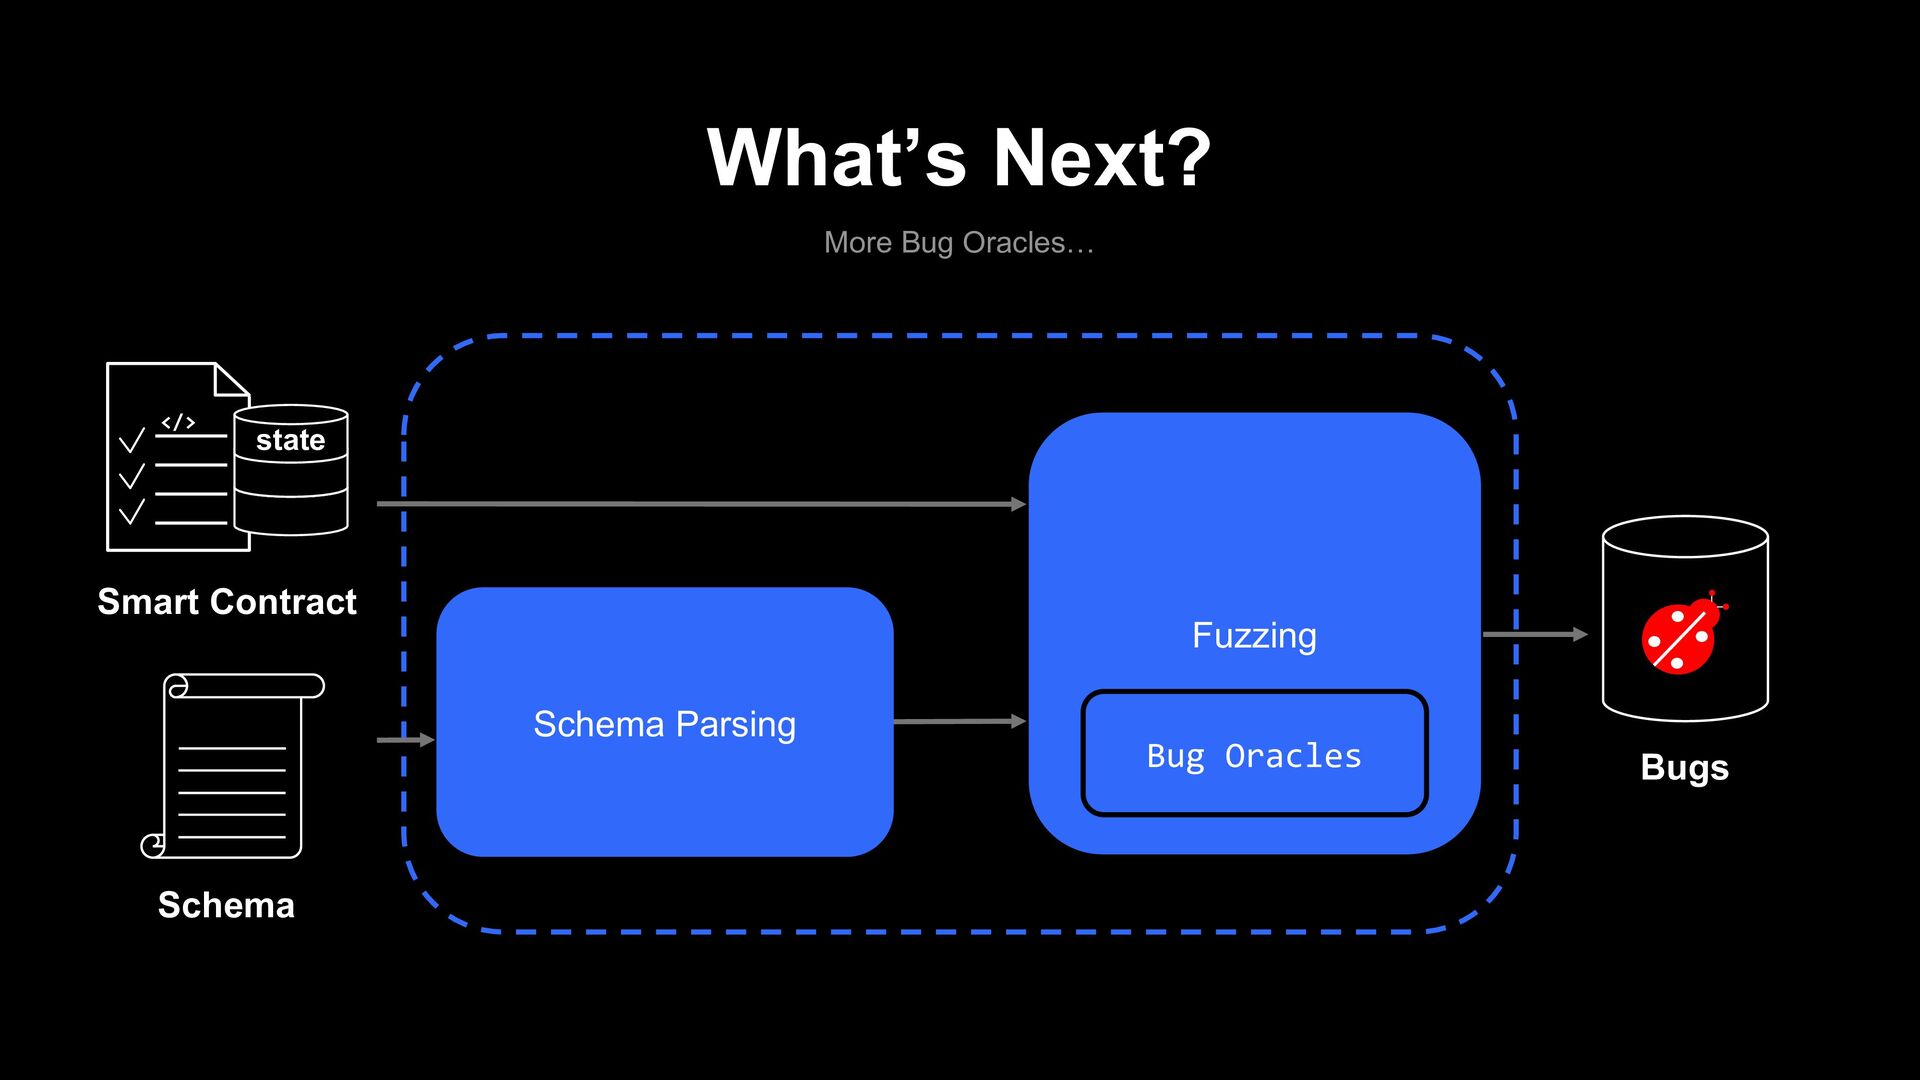
Design Bug Oracle › We basically detect a runtime error
which occurs during execution time. › Gas depletion due to lack of gas. › Panic including assertion failure, integer overflow. › Out of bound error when accessing an array that exceeds its size. › … › We currently support to detect only runtime errors. -
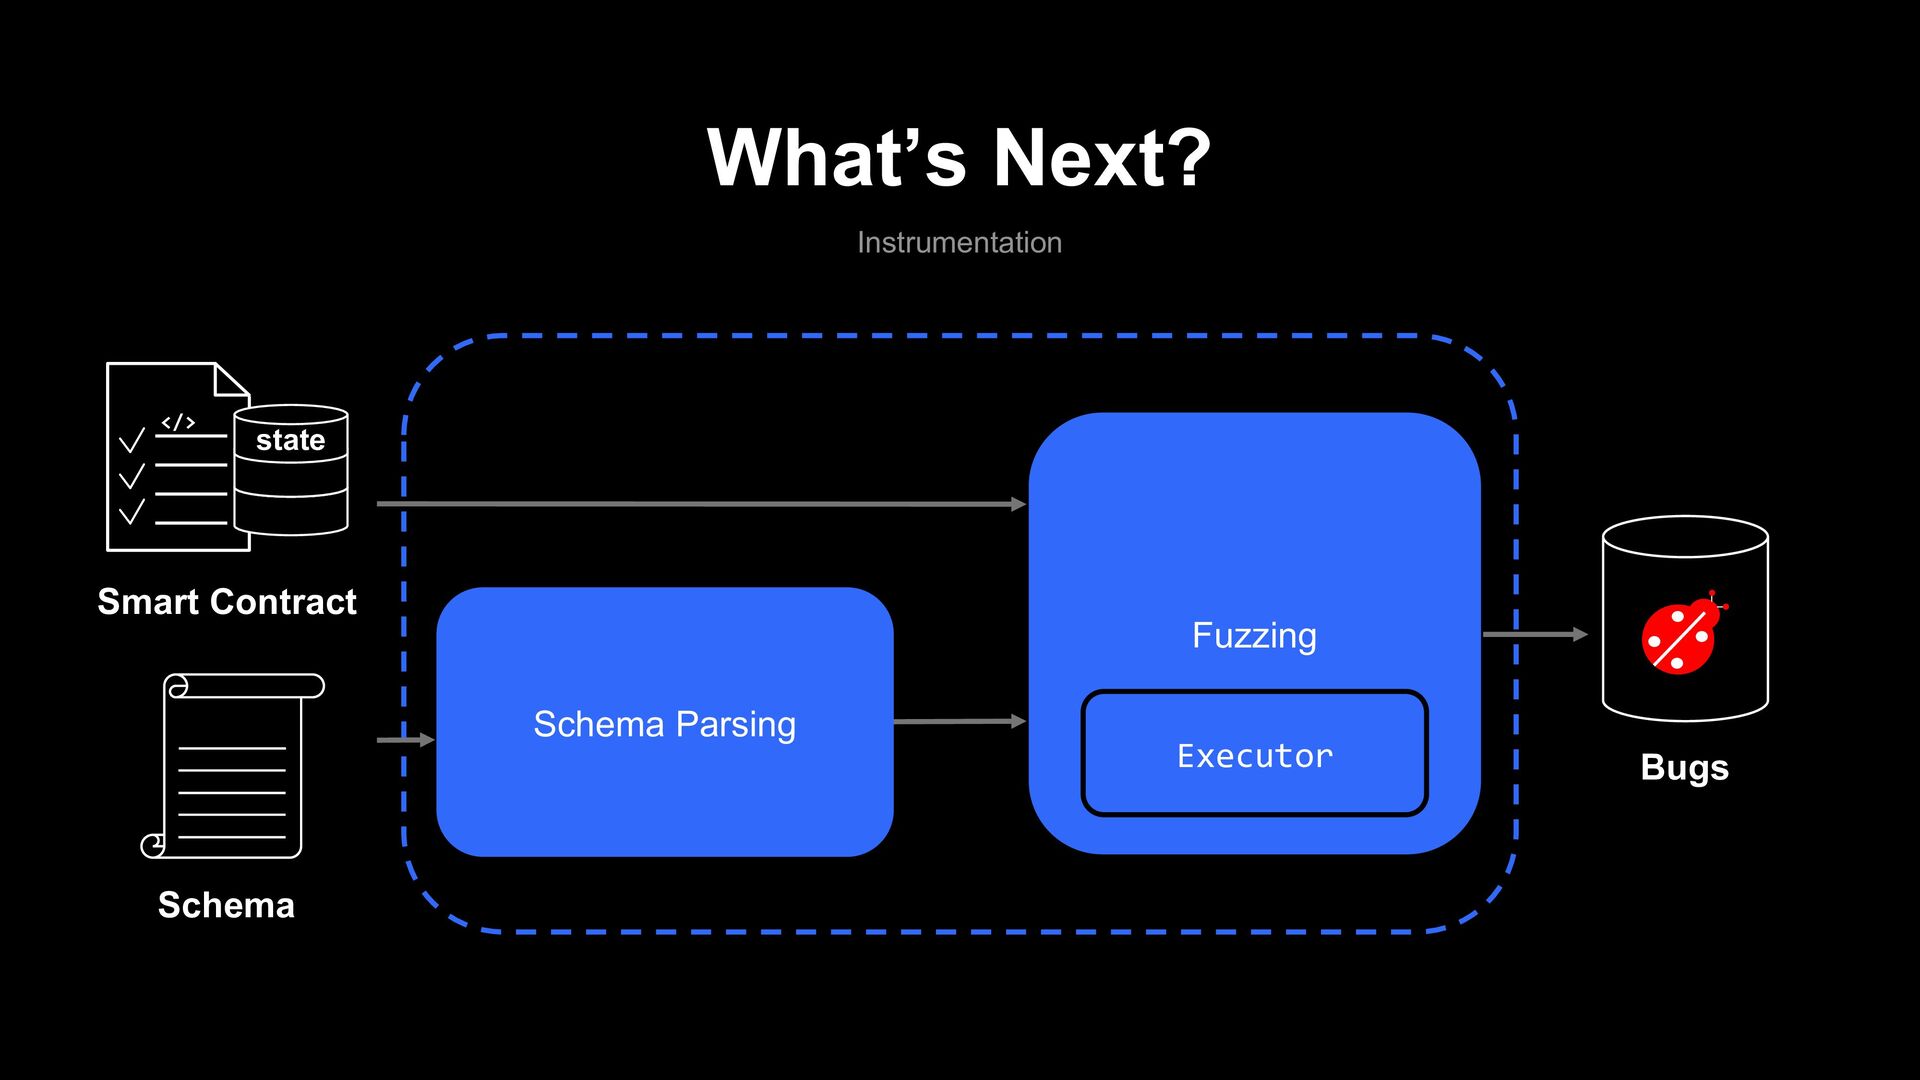
What’s Next? Schema Bugs Instrumentation </> state Smart Contract Schema
Parsing Fuzzing Executor -
What’s Next? Schema Bugs More Bug Oracles… </> state Smart
Contract Schema Parsing Fuzzing Bug Oracles -
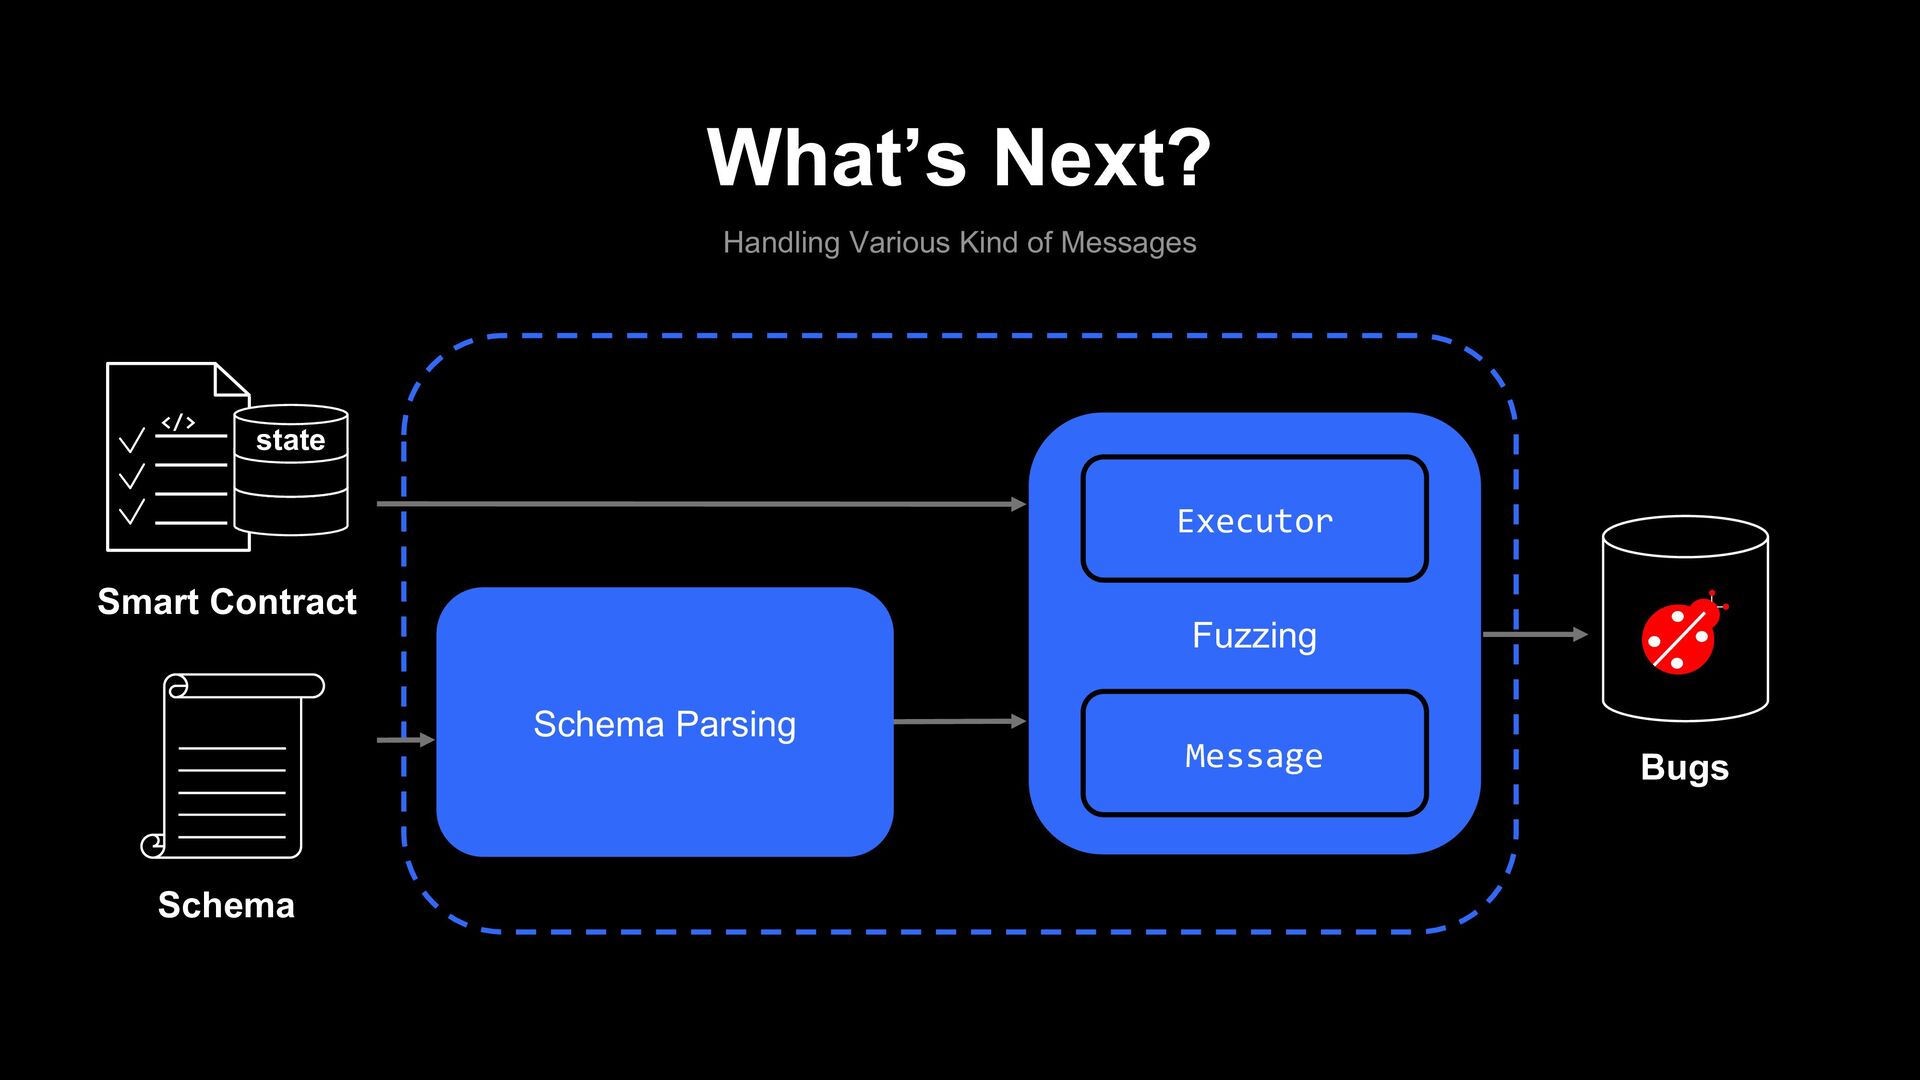
What’s Next? Schema Bugs Handling Various Kind of Messages </>
state Smart Contract Schema Parsing Fuzzing Message Executor -
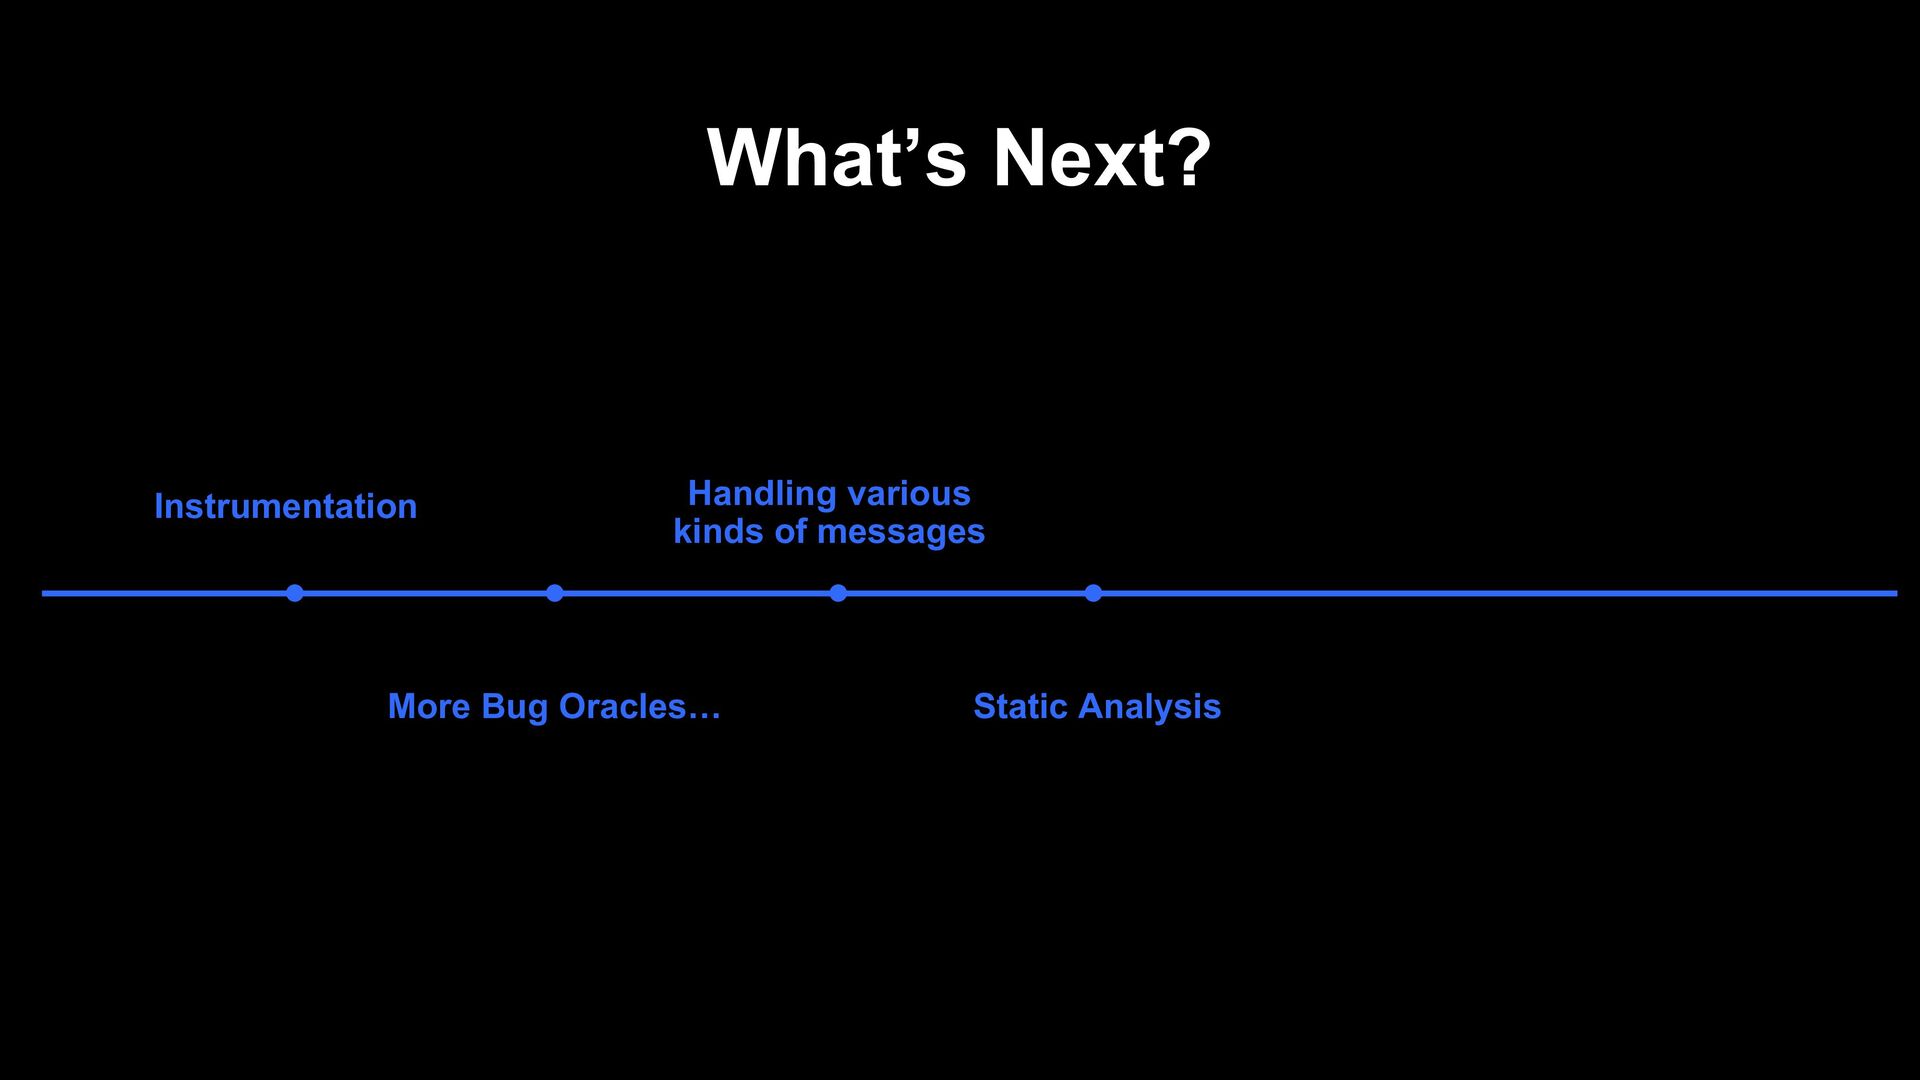
Static Analysis More Bug Oracles… Handling various kinds of messages
Instrumentation What’s Next? -
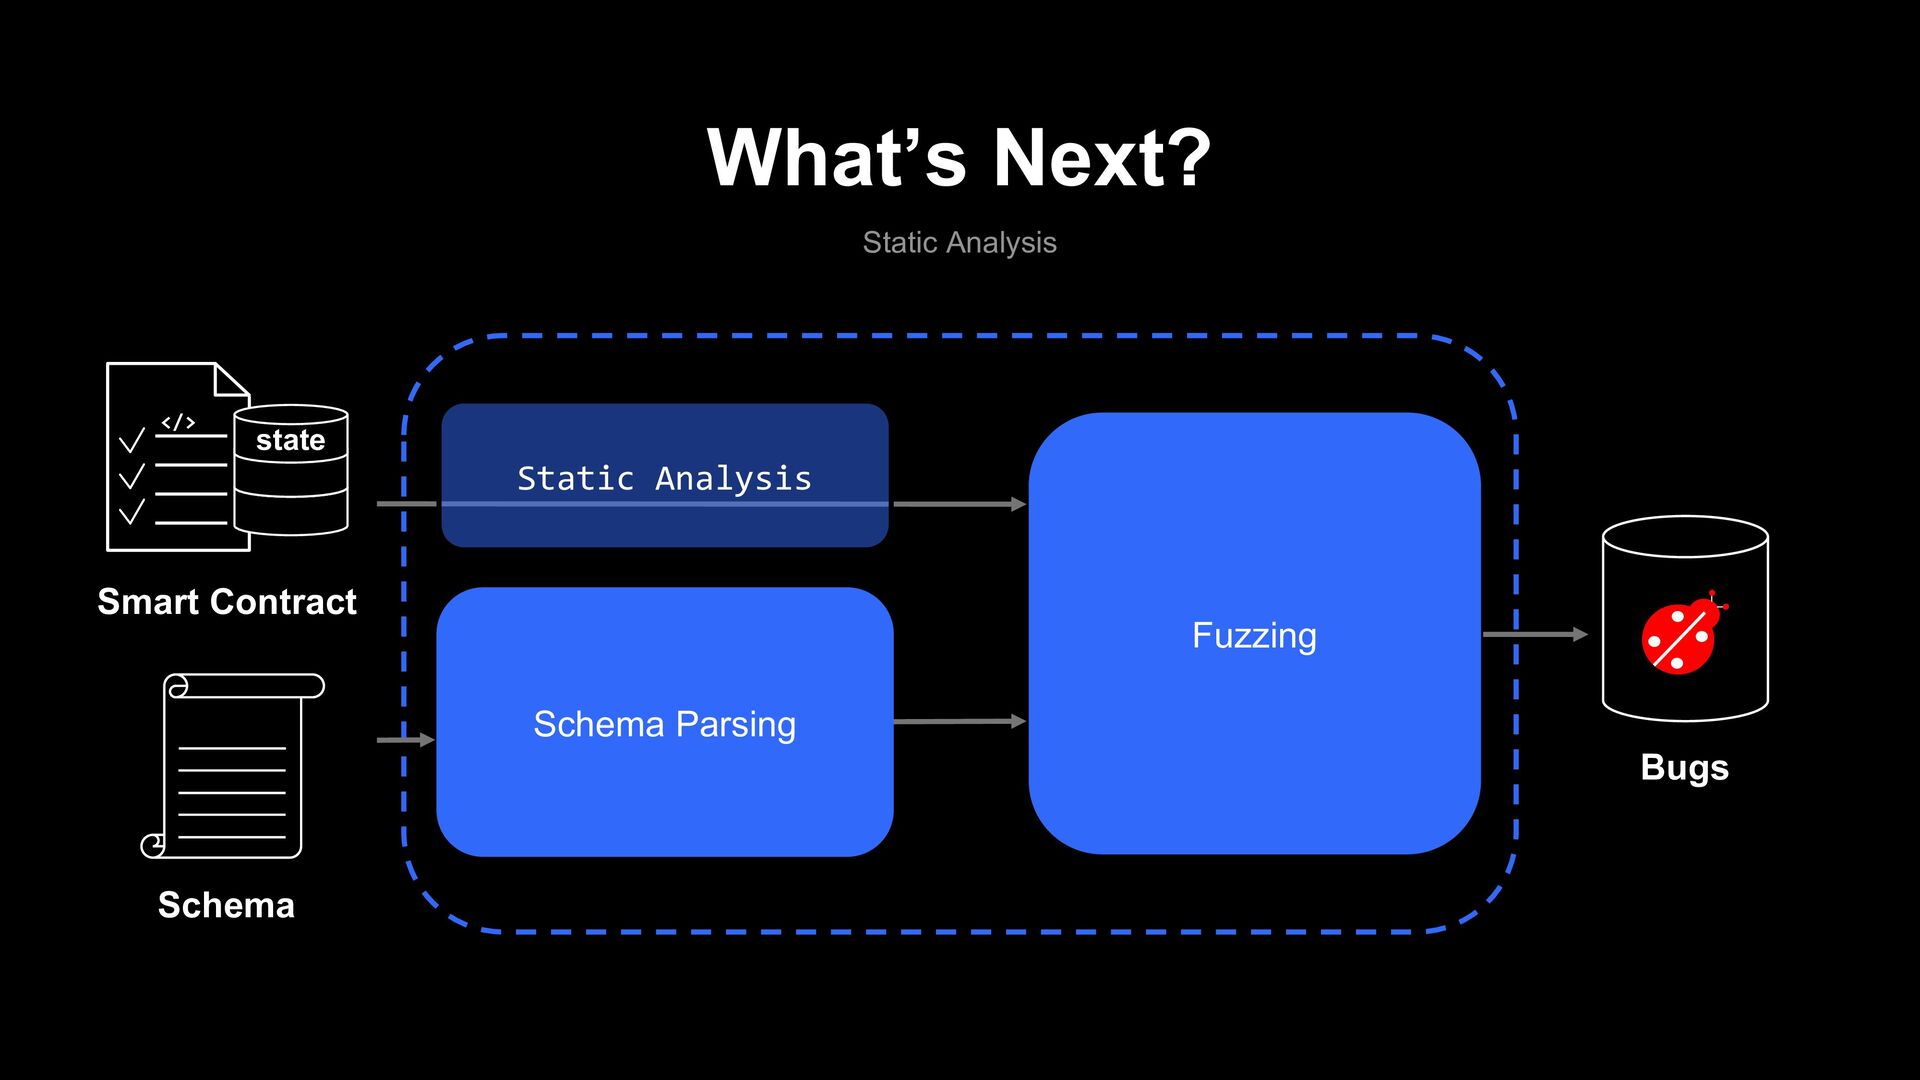
What’s Next? Schema Bugs Static Analysis </> state Smart Contract
Schema Parsing Fuzzing Static Analysis -
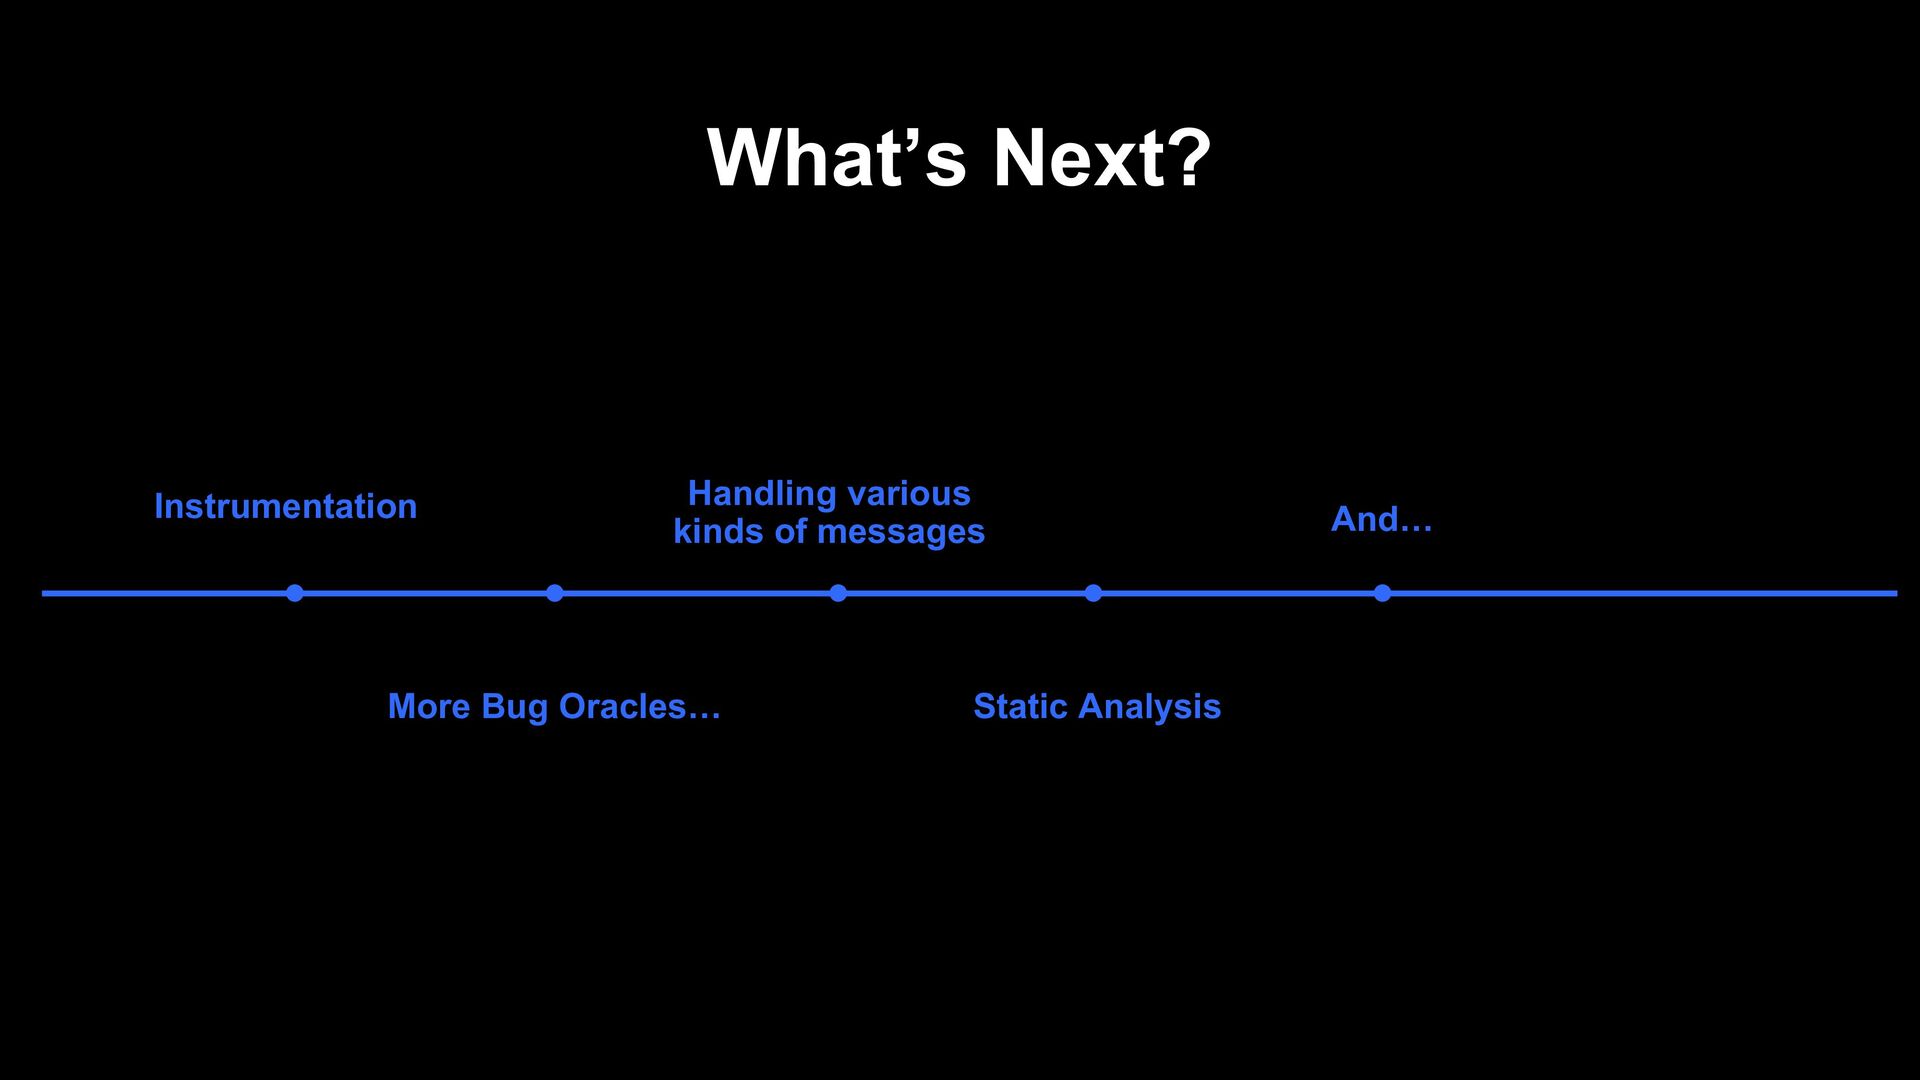
Static Analysis More Bug Oracles… And… Handling various kinds of
messages Instrumentation What’s Next?