Share
La sécurité dans l'IoT : difficultés, failles et contre-mesures @VoxxedDayLU
Avec la multiplication des objets connectés dans notre quotidien, la sécurité de ces appareils électroniques, qui a été souvent négligée par le passé, devient une réelle problématique. Leur faible coût de conception, la négligence des fabricants ou même la notre, nous développeurs, en font des proies faciles pour les hackers.
Ce phénomène se constate bien dans l'actualité, où l'on parle de plus en plus d'attaques à grande échelles visant des cameras ou frigos connectés, mais également les serrures Bluetooth.
Au cours de ce talk nous verrons en détails le principe des dernières attaques qui ont fait la une. Nous parlerons ensuite des failles touchant les IoTs les plus courantes (le top 10 OWASP IoT), les solutions et contre-mesures.
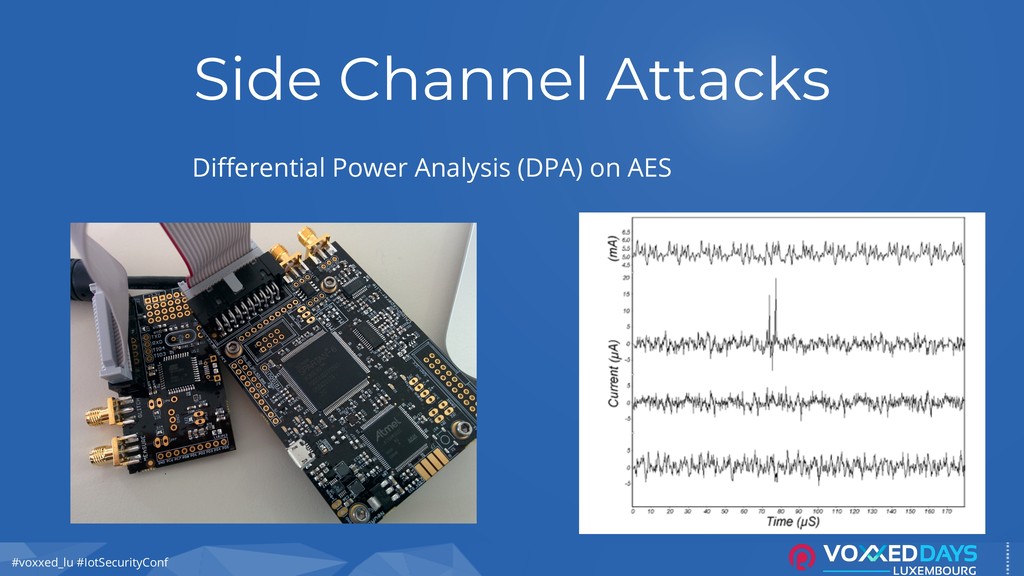
Nous parlerons notamment des attaques par canaux auxiliaires pour lesquelles peu de solutions existent et qui donnent toujours du fil à retordre aux chercheurs.
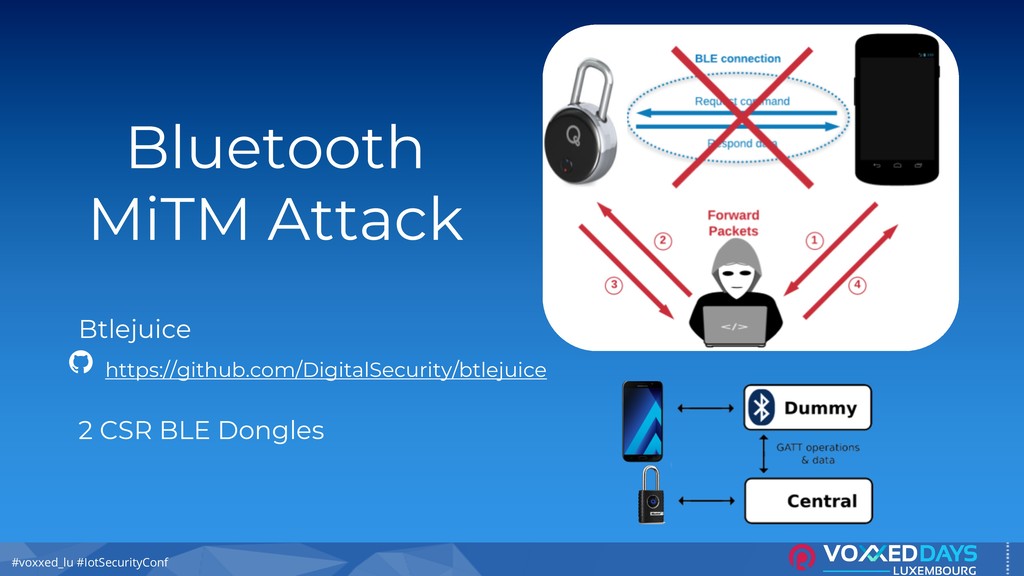
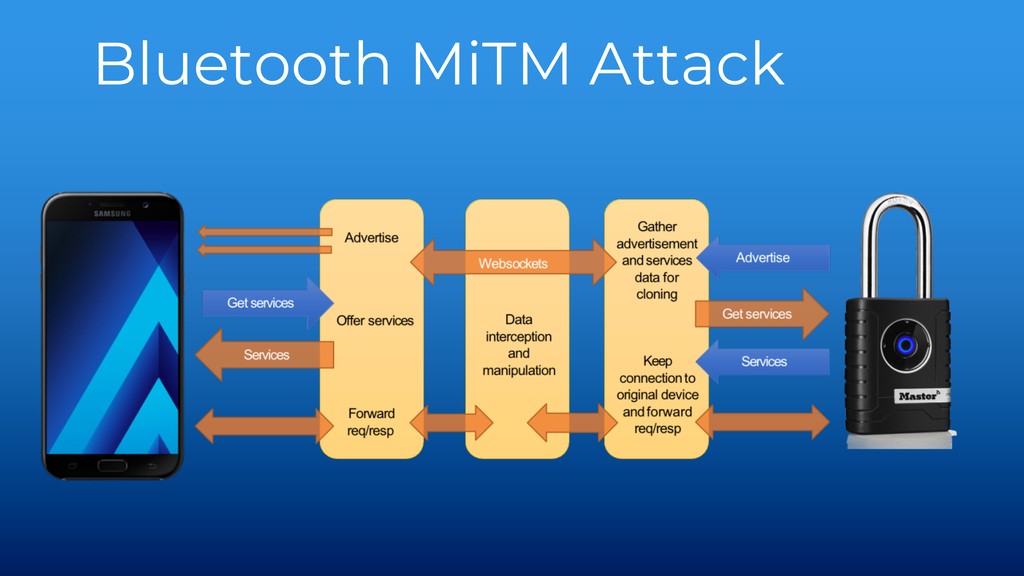
Enfin, nous terminerons par une petite démo d’attaque de type Man-in-the-midle (MiTM) sur un objet Bluetooth.
Alexis DUQUE
Transcript
67 slides
-
#DevoxxFR #voxxed_lu #IotSecurityConf La sécurité dans l'IoT : difficultés, failles
et contre-mesures Alexis DUQUE @alexis0duque -
#voxxed_lu #IotSecurityConf About Me ALEXIS DUQUE Embedded Software engineer &
R&D leader at Rtone PhD Student at CITI Lab, INSA de Lyon @alexis0duque #IoTSecurityConf alexisduque [email protected] alexisduque.me https://goo.gl/oNUWu6 -
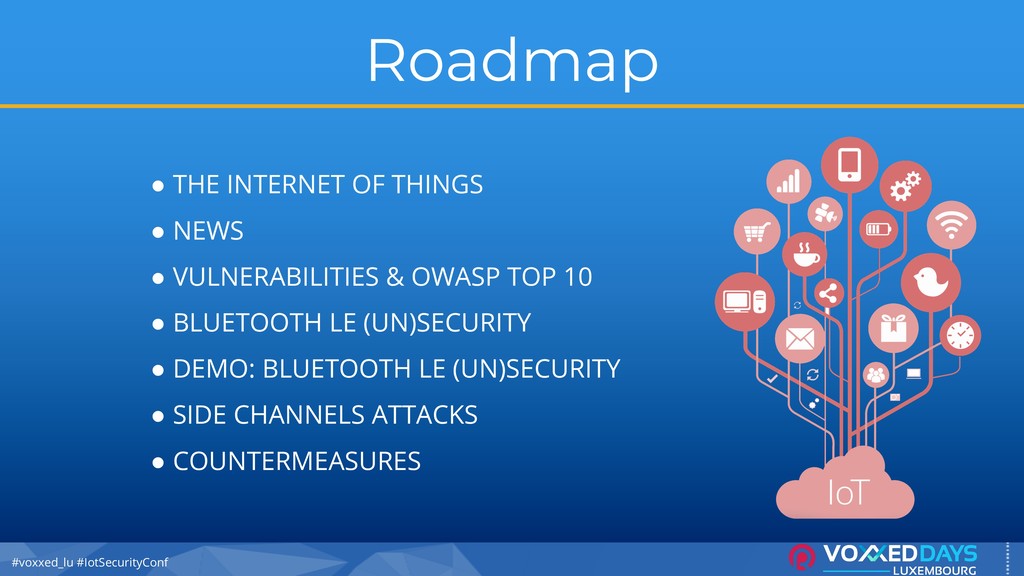
#voxxed_lu #IotSecurityConf Roadmap • THE INTERNET OF THINGS • NEWS
• VULNERABILITIES & OWASP TOP 10 • BLUETOOTH LE (UN)SECURITY • DEMO: BLUETOOTH LE (UN)SECURITY • SIDE CHANNELS ATTACKS • COUNTERMEASURES -
#voxxed_lu #IotSecurityConf IoT Security ? • Uncontrolled Environment • Heterogeneity
• Users and Manufacturers not aware of security risks • Surface of attacks: hardware + software • Scalability • Constrained Resources -
#voxxed_lu #IotSecurityConf IoT+Security Challenges • Objects are small and everywhere
and connected • Prone to environmental influences • Weak calculation and memory (limited for crypto) • They are autonomous • Cyber attacks have real world consequences -
#voxxed_lu #IotSecurityConf Attack Surface Area Around 20 attack surface areas
on the OWASP IoT Project E.g. web Interfaces, physical interfaces, firmware, network, cloud, mobile, API, etc Each attack surface has multiple potential vulnerabilities Firmware packages use old and/or unsupported versions of 3rd party components -
#voxxed_lu #IotSecurityConf Firmware Update • Need to be able to
update firmware • Automatic updates? • Needs to be tested on all hardware variants • Download path needs to be secure • Update path needs to be secure -
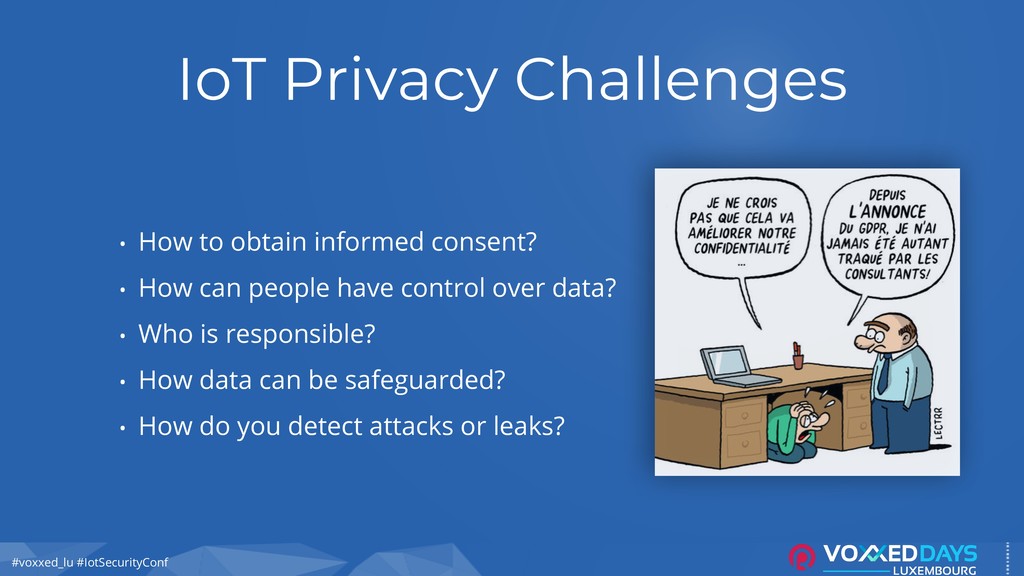
#voxxed_lu #IotSecurityConf IoT Privacy Challenges • How to obtain informed
consent? • How can people have control over data? • Who is responsible? • How data can be safeguarded? • How do you detect attacks or leaks? -
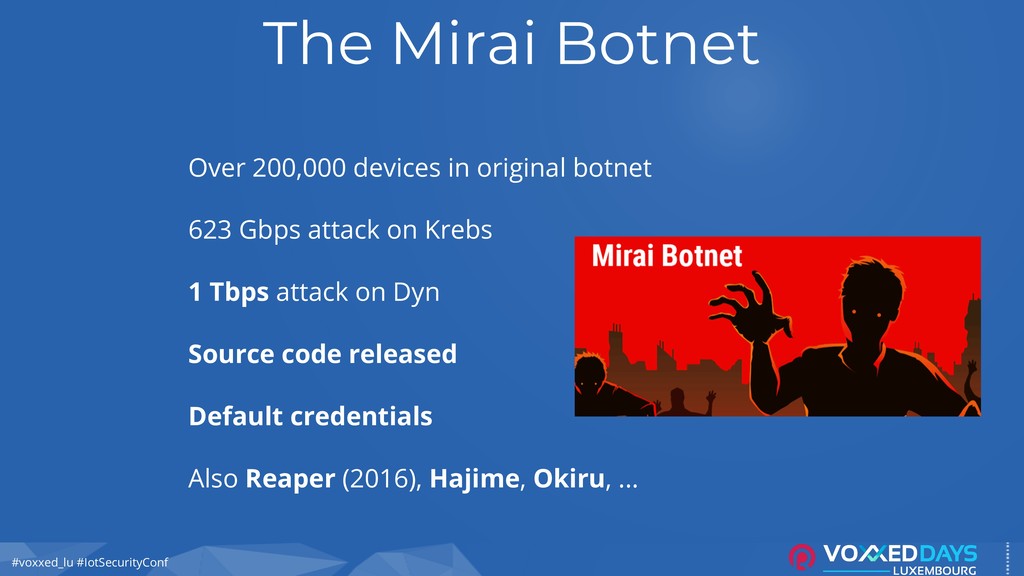
#voxxed_lu #IotSecurityConf The Mirai Botnet Over 200,000 devices in original
botnet 623 Gbps attack on Krebs 1 Tbps attack on Dyn Source code released Default credentials Also Reaper (2016), Hajime, Okiru, ... -
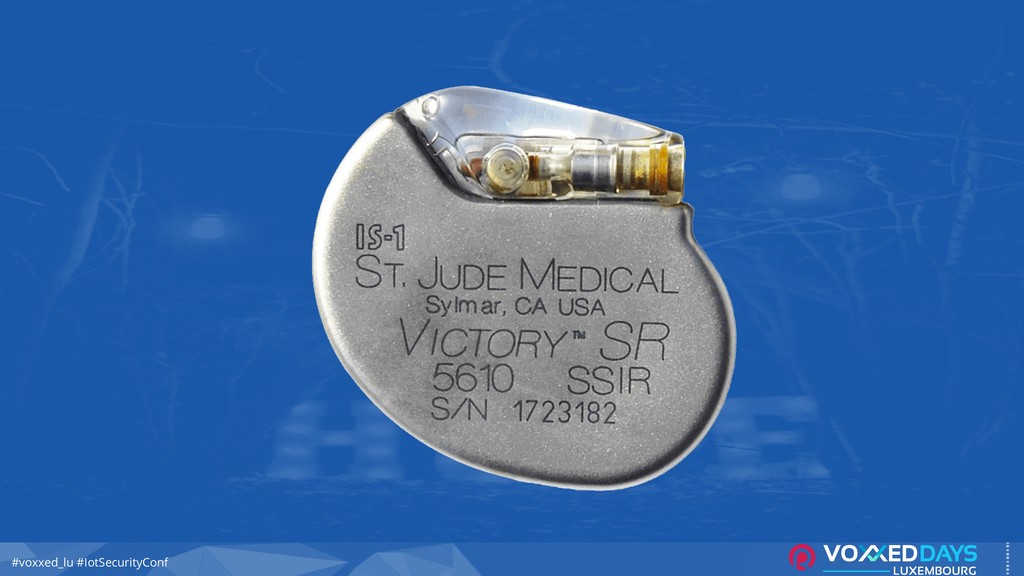
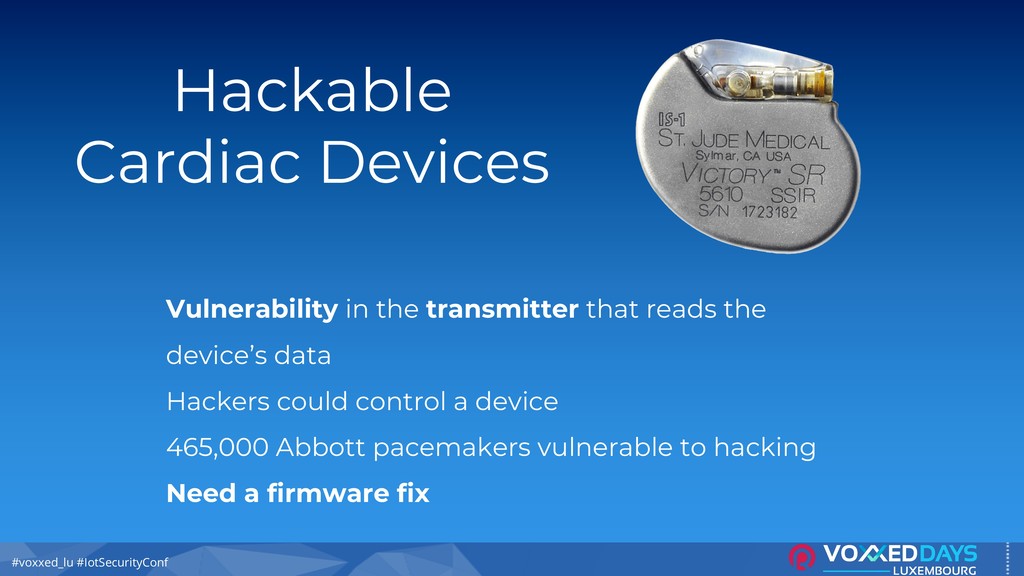
#voxxed_lu #IotSecurityConf Hackable Cardiac Devices Vulnerability in the transmitter that
reads the device’s data Hackers could control a device 465,000 Abbott pacemakers vulnerable to hacking Need a firmware fix -
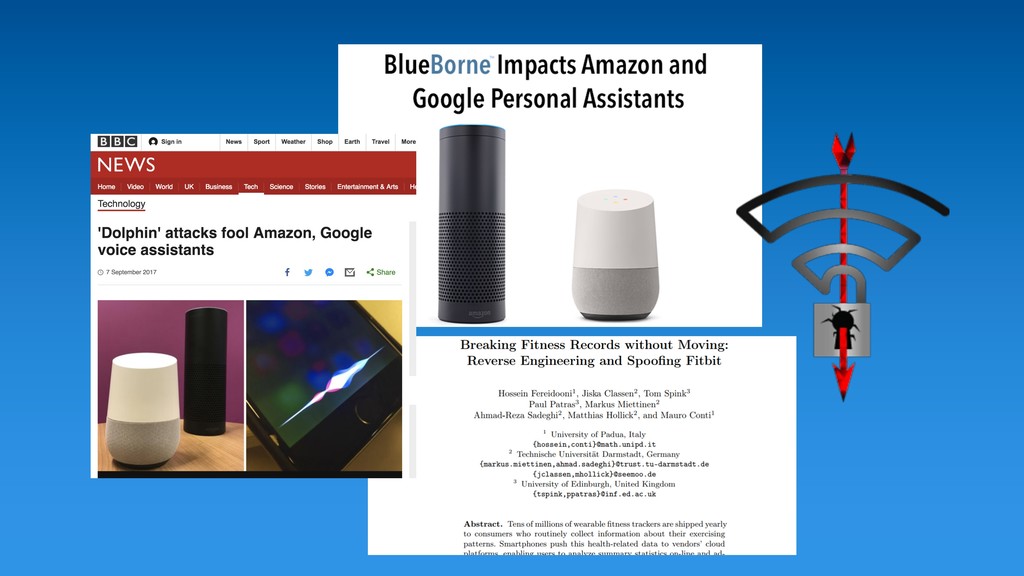
#voxxed_lu #IotSecurityConf Bluetooth Vulnerabilities BlueBorne https://www.armis.com/blueborne/ Android, Windows, iOS &
Linux Amazon Echo and Google Home 8 vulnerabilities -
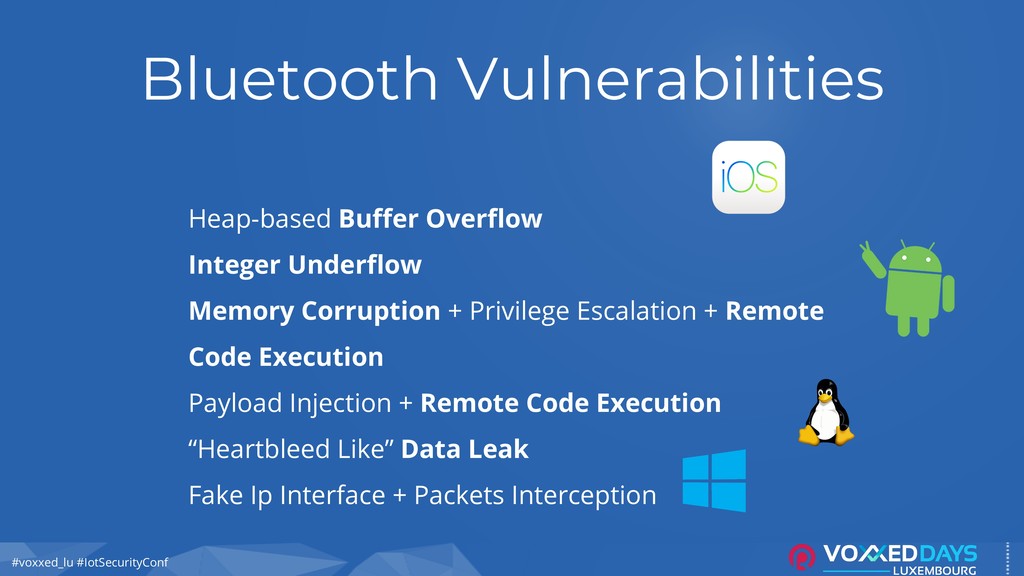
#voxxed_lu #IotSecurityConf Bluetooth Vulnerabilities Heap-based Buffer Overflow Integer Underflow Memory
Corruption + Privilege Escalation + Remote Code Execution Payload Injection + Remote Code Execution “Heartbleed Like” Data Leak Fake Ip Interface + Packets Interception -
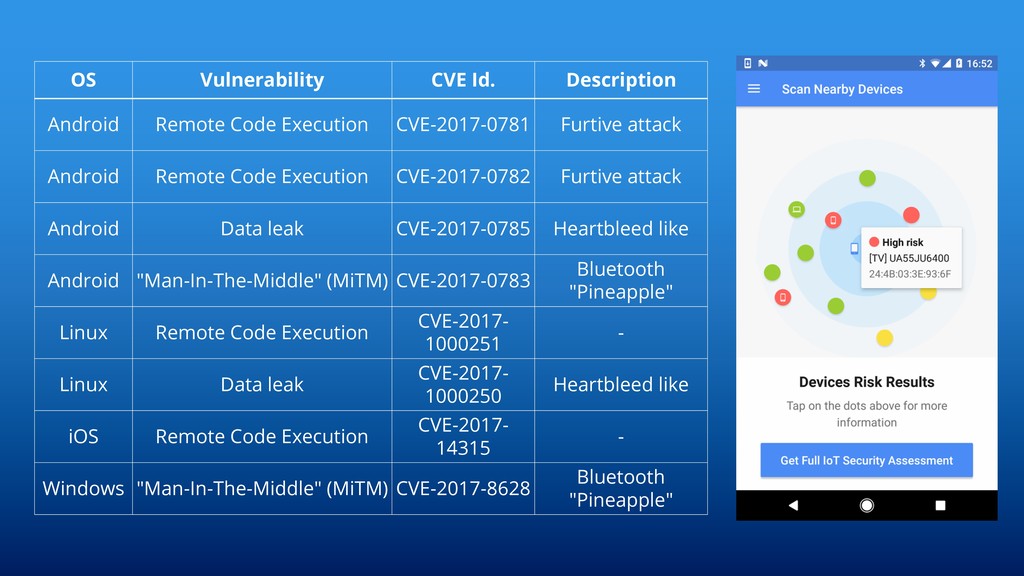
OS Vulnerability CVE Id. Description Android Remote Code Execution CVE-2017-0781
Furtive attack Android Remote Code Execution CVE-2017-0782 Furtive attack Android Data leak CVE-2017-0785 Heartbleed like Android "Man-In-The-Middle" (MiTM) CVE-2017-0783 Bluetooth "Pineapple" Linux Remote Code Execution CVE-2017- 1000251 - Linux Data leak CVE-2017- 1000250 Heartbleed like iOS Remote Code Execution CVE-2017- 14315 - Windows "Man-In-The-Middle" (MiTM) CVE-2017-8628 Bluetooth "Pineapple" -
#voxxed_lu #IotSecurityConf What Is OWASP? [owasp.org] “The Open Web Application
Security Project (OWASP) is a worldwide not-for-profit charitable organization focused on improving the security of software” [owasp.org] “The OWASP Internet of Things Project is designed to help manufacturers, developers, and consumers better understand the security issues associated with the Internet of Things, and to enable users in any context to make better security decisions when building, deploying, or assessing IoT technologies” -
#voxxed_lu #IotSecurityConf OWASP IoT Top 10 1. Insecure Web Interface
2. Insufficient Authentication/Authorization 3. Insecure Network Services 4. Lack of Transport Encryption/Integrity Verification 5. Privacy Concerns 6. Insecure Cloud Interface 7. Insecure Mobile Interface 8. Insufficient Security Configurability 9. Insecure Software/Firmware 10.Poor Physical Security -
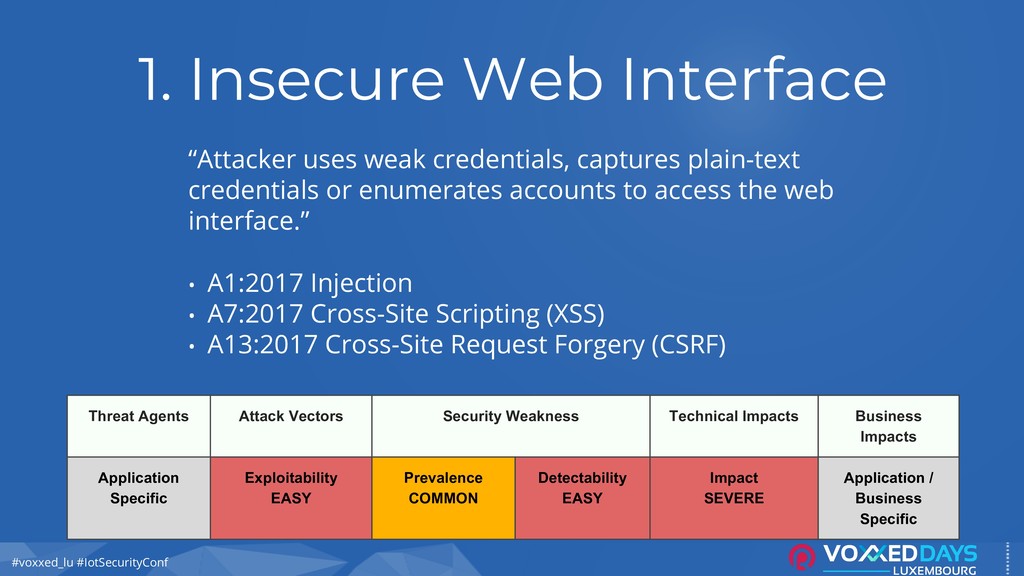
#voxxed_lu #IotSecurityConf 1. Insecure Web Interface “Attacker uses weak credentials,
captures plain-text credentials or enumerates accounts to access the web interface.” • A1:2017 Injection • A7:2017 Cross-Site Scripting (XSS) • A13:2017 Cross-Site Request Forgery (CSRF) Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability EASY Prevalence COMMON Detectability EASY Impact SEVERE Application / Business Specific -
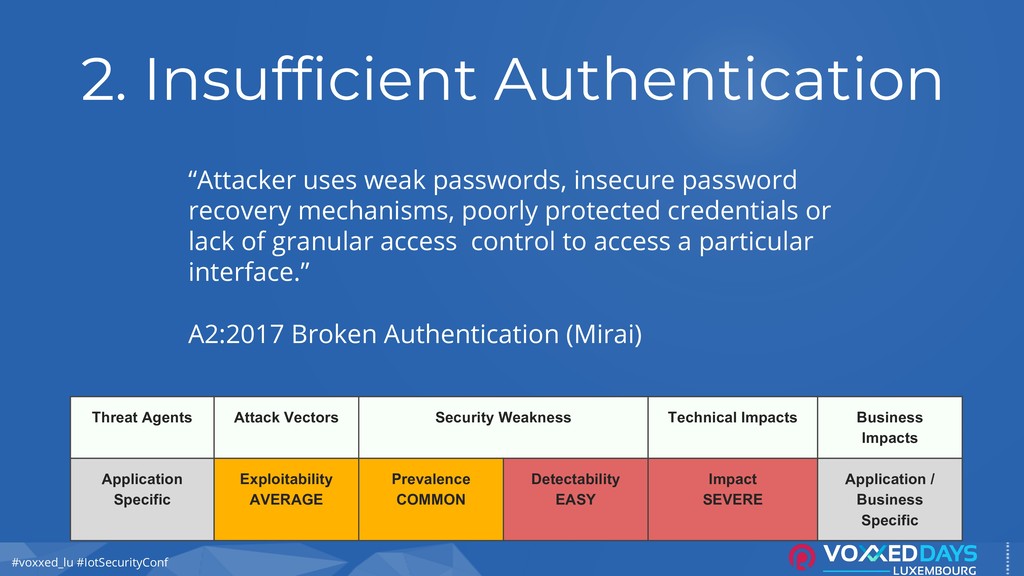
#voxxed_lu #IotSecurityConf 2. Insufficient Authentication “Attacker uses weak passwords, insecure
password recovery mechanisms, poorly protected credentials or lack of granular access control to access a particular interface.” A2:2017 Broken Authentication (Mirai) Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability AVERAGE Prevalence COMMON Detectability EASY Impact SEVERE Application / Business Specific -
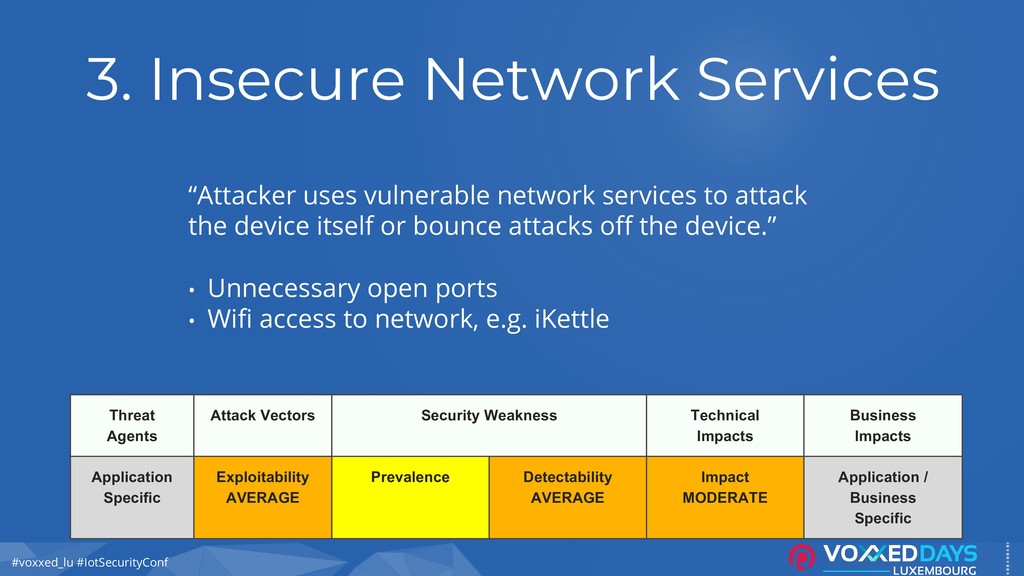
#voxxed_lu #IotSecurityConf Threat Agents Attack Vectors Security Weakness Technical Impacts
Business Impacts Application Specific Exploitability AVERAGE Prevalence Detectability AVERAGE Impact MODERATE Application / Business Specific 3. Insecure Network Services “Attacker uses vulnerable network services to attack the device itself or bounce attacks off the device.” • Unnecessary open ports • Wifi access to network, e.g. iKettle -
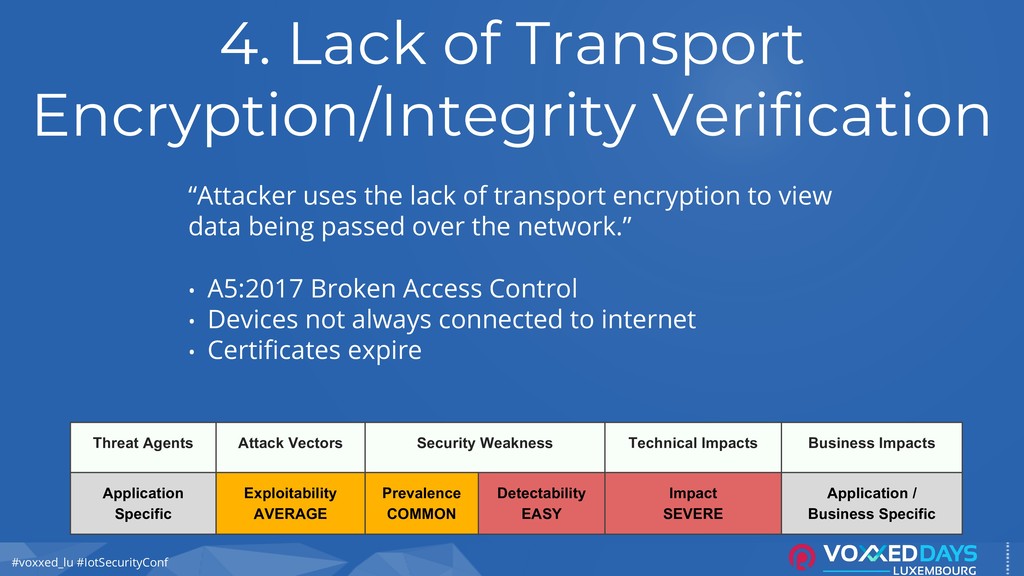
#voxxed_lu #IotSecurityConf 4. Lack of Transport Encryption/Integrity Verification “Attacker uses
the lack of transport encryption to view data being passed over the network.” • A5:2017 Broken Access Control • Devices not always connected to internet • Certificates expire Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability AVERAGE Prevalence COMMON Detectability EASY Impact SEVERE Application / Business Specific -
#voxxed_lu #IotSecurityConf 5. Privacy Concerns “Attacker uses multiple vectors such
as insufficient authentication, lack of transport encryption or insecure network services to view personal data which is not being properly protected or is being collected unnecessarily.” • EU General Data Protection Regulation (GDPR) - 25th May 2018 • Requirements for User Consent and Pseudonymisation. • Legal obligation to notify the Supervisory Authority of data breach without undue delay (72 hours?) Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability AVERAGE Prevalence COMMON Detectability EASY Impact SEVERE Application / Business Specific -
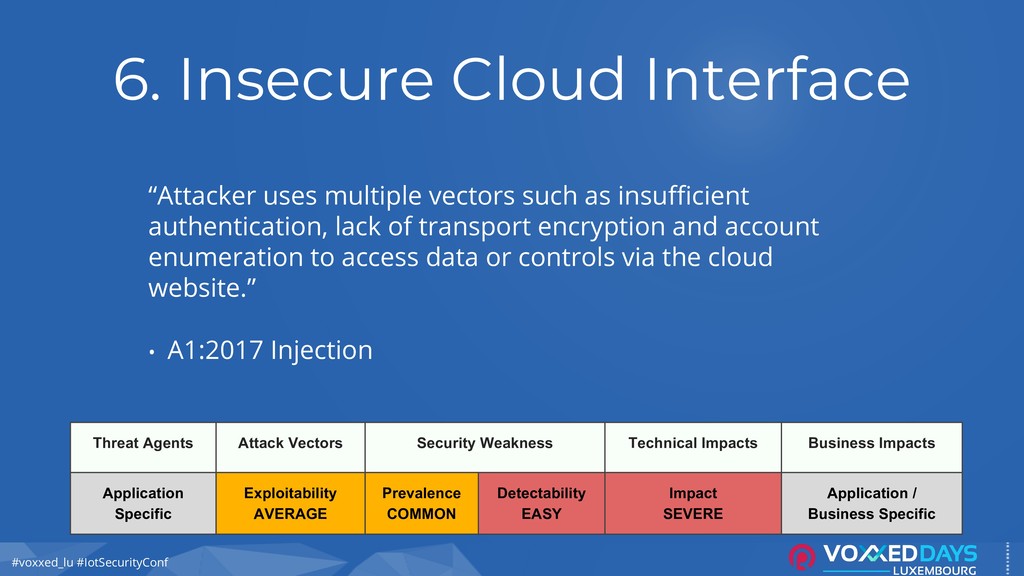
#voxxed_lu #IotSecurityConf 6. Insecure Cloud Interface “Attacker uses multiple vectors
such as insufficient authentication, lack of transport encryption and account enumeration to access data or controls via the cloud website.” • A1:2017 Injection Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability AVERAGE Prevalence COMMON Detectability EASY Impact SEVERE Application / Business Specific -
#voxxed_lu #IotSecurityConf 7. Insecure Mobile Interface “Attacker uses multiple vectors
such as insufficient authentication, lack of transport encryption and account enumeration to access data or controls via the mobile interface.” • No best practice? • National Institute of Standards and Technology (NIST) “Guide to Bluetooth Security” Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability AVERAGE Prevalence COMMON Detectability EASY Impact SEVERE Application / Business Specific -
#voxxed_lu #IotSecurityConf 8. Insufficient Security Configurability “Attacker uses the lack
of granular permissions to access data or controls on the device. The attacker could also us the lack of encryption options and lack of password options to perform other attacks which lead to compromise of the device and/or data.” Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability AVERAGE Prevalence COMMON Detectability EASY Impact MODERATE Application / Business Specific -
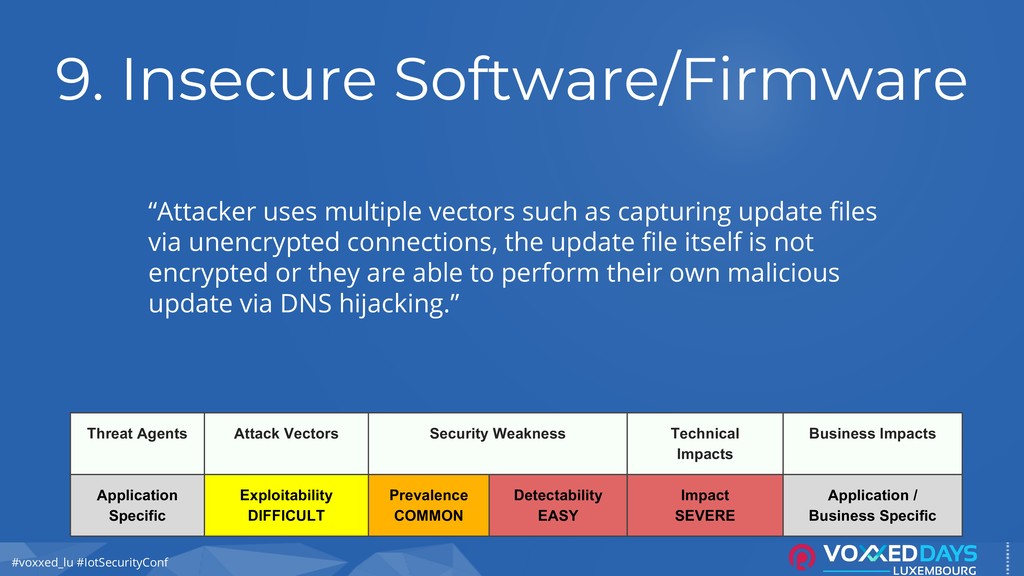
#voxxed_lu #IotSecurityConf 9. Insecure Software/Firmware “Attacker uses multiple vectors such
as capturing update files via unencrypted connections, the update file itself is not encrypted or they are able to perform their own malicious update via DNS hijacking.” Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability DIFFICULT Prevalence COMMON Detectability EASY Impact SEVERE Application / Business Specific -
#voxxed_lu #IotSecurityConf 10. Poor Physical Security “Attacker uses vectors such
as USB ports or other storage means to access the Operating System and potentially any data stored on the device.” • JTAG • Serial bus spy: BUS PIRATE • Oscilloscope Threat Agents Attack Vectors Security Weakness Technical Impacts Business Impacts Application Specific Exploitability AVERAGE Prevalence COMMON Detectability AVERAGE Impact SEVERE Application / Business Specific -
#voxxed_lu #IotSecurityConf Bluetooth LE Bluetooth Low Energy, BLE, Bluetooth 4/5,
Bluetooth SMART One of most exploding recently IoT technologies Completely different than previous Bluetooth 2, 3 (BR/EDR) Designed for low energy usage, simplicity rather than throughput -
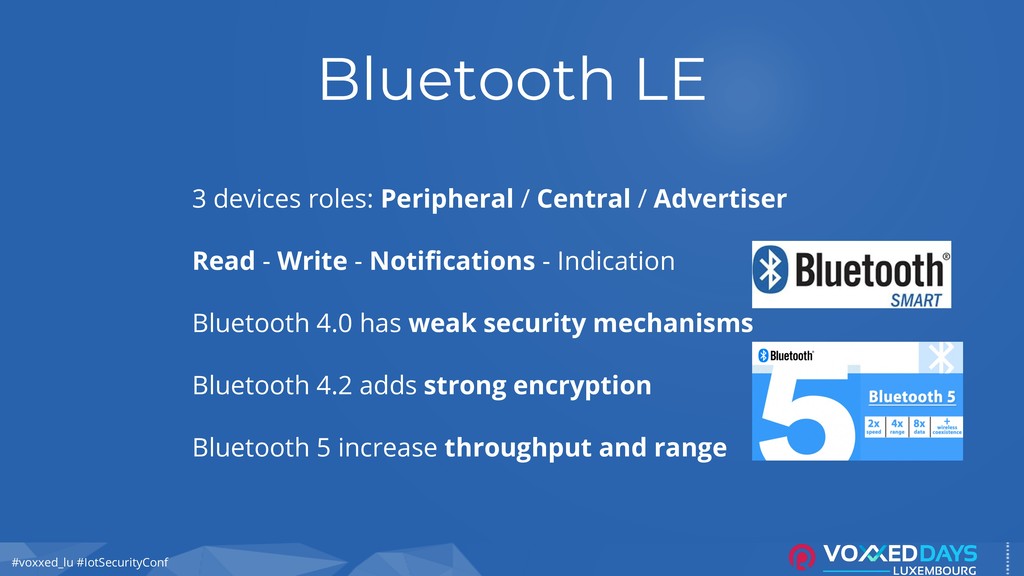
#voxxed_lu #IotSecurityConf Bluetooth LE 3 devices roles: Peripheral / Central
/ Advertiser Read - Write - Notifications - Indication Bluetooth 4.0 has weak security mechanisms Bluetooth 4.2 adds strong encryption Bluetooth 5 increase throughput and range -
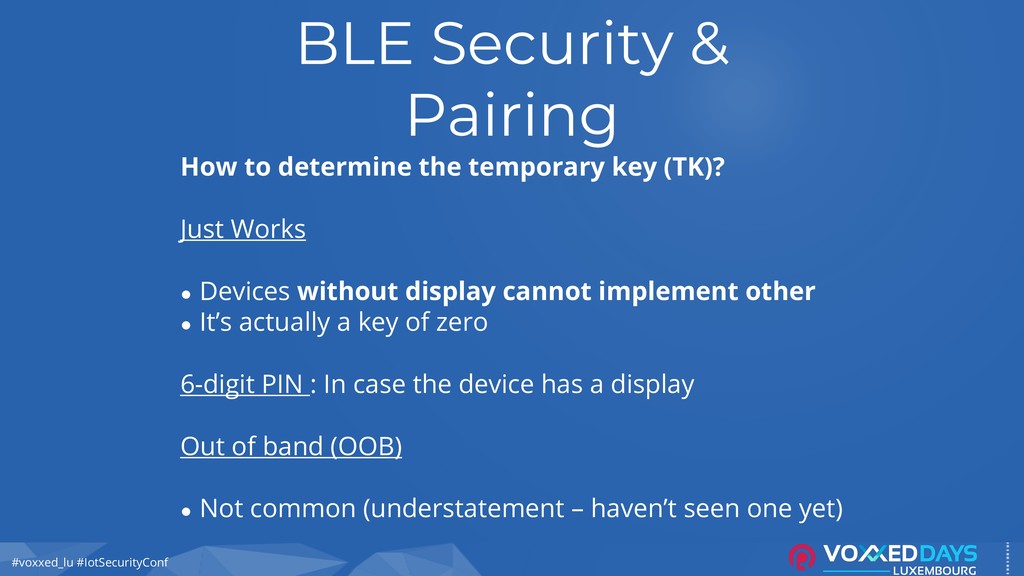
#voxxed_lu #IotSecurityConf BLE Security & Pairing Uses AES-128 with CCM
(Counter with CBC-MAC) encryption Uses Diffie-Hellman Key Distribution to share various keys • Identity Resolving Key is used for privacy (IRK) • Signing Resolving Key provides fast authentication without encryption (SRK) • Long Term Key is used (LTK) Pairing encrypts the link using a Temporary Key (TK) • Derived from passkey & then distribute keys -
#voxxed_lu #IotSecurityConf BLE Security & Pairing How to determine the
temporary key (TK)? Just Works • Devices without display cannot implement other • It’s actually a key of zero 6-digit PIN : In case the device has a display Out of band (OOB) • Not common (understatement – haven’t seen one yet) -
#voxxed_lu #IotSecurityConf Bluetooth Core Specification “None of the pairing methods
provide protection against a passive eavesdropper” -
#voxxed_lu #IotSecurityConf Bluetooth 4.2 Security 4.2 brings strong encryption with
Elliptic Curves Diffie-Hellman (ECDH) with LE Secure Connection Numeric Comparison to determine the TK In practice, ~80% of tested devices do not implement BLE-layer encryption -
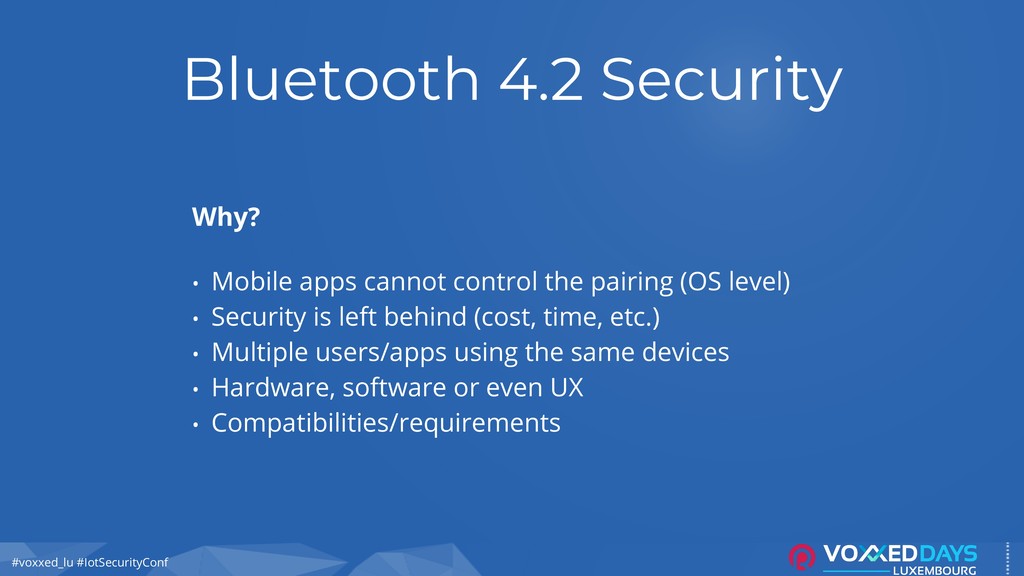
#voxxed_lu #IotSecurityConf Bluetooth 4.2 Security Why? • Mobile apps cannot
control the pairing (OS level) • Security is left behind (cost, time, etc.) • Multiple users/apps using the same devices • Hardware, software or even UX • Compatibilities/requirements -
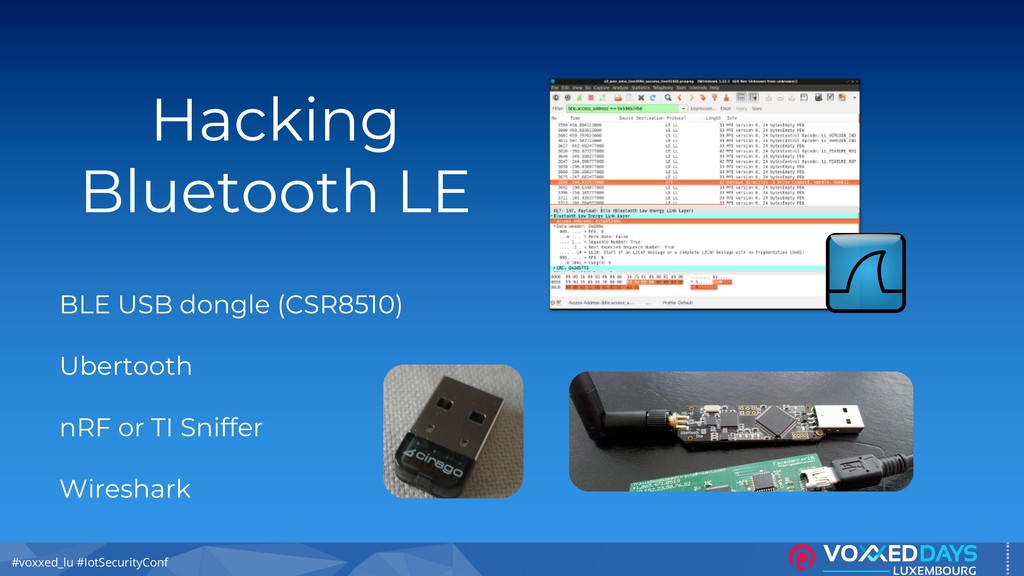
#voxxed_lu #IotSecurityConf Hacking Bluetooth LE BLE USB dongle (CSR8510) Ubertooth
nRF or TI Sniffer Wireshark -
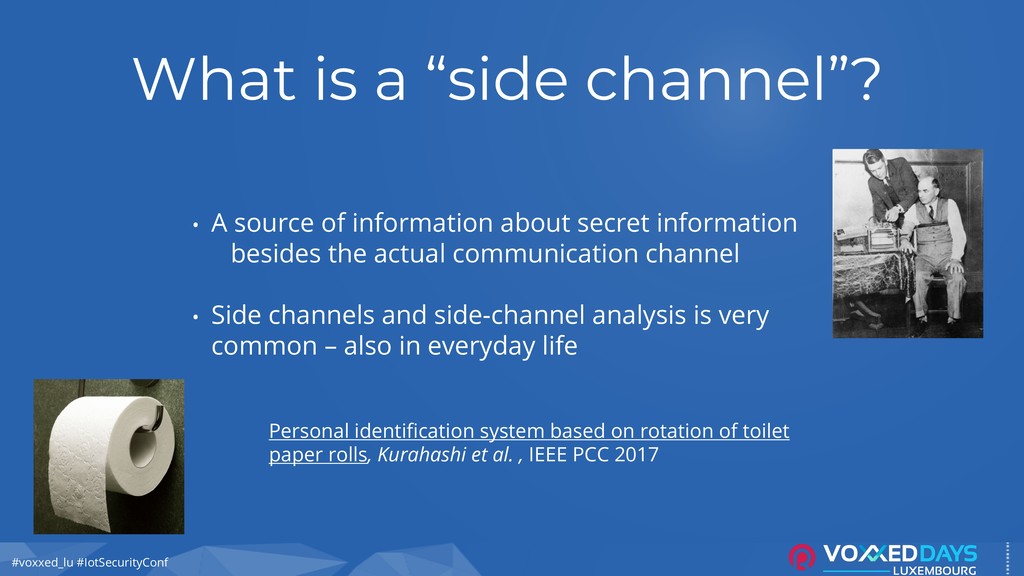
#voxxed_lu #IotSecurityConf What is a “side channel”? • A source
of information about secret information besides the actual communication channel • Side channels and side-channel analysis is very common – also in everyday life Personal identification system based on rotation of toilet paper rolls, Kurahashi et al. , IEEE PCC 2017 -
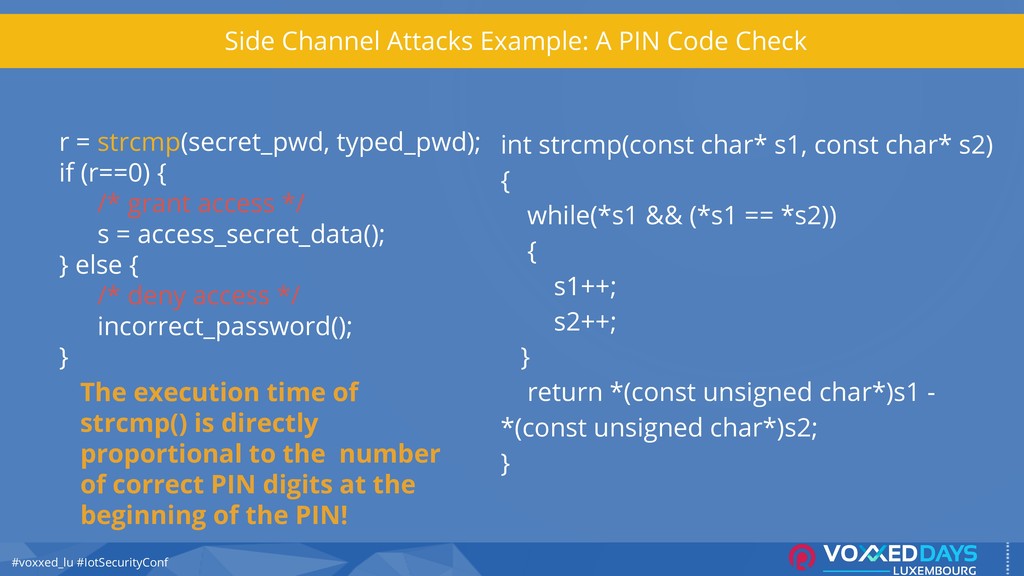
#voxxed_lu #IotSecurityConf Side Channel Attacks Example: A PIN Code Check
r = strcmp(secret_pwd, typed_pwd); if (r==0) { /* grant access */ s = access_secret_data(); } else { /* deny access */ incorrect_password(); } int strcmp(const char* s1, const char* s2) { while(*s1 && (*s1 == *s2)) { s1++; s2++; } return *(const unsigned char*)s1 - *(const unsigned char*)s2; } The execution time of strcmp() is directly proportional to the number of correct PIN digits at the beginning of the PIN! -
#voxxed_lu #IotSecurityConf IoT Security Best Practises Security objectives must be
considered during the product life cycle! • Security “by design” • Risks analysis • Technologies choices and their threat • Architecture requirements for security • Integration in the project workflow • Security review during the project -
#voxxed_lu #IotSecurityConf IoT Security Best Practises Cover the main risks!
• Security Upgrade • Communications encryption and authentication • Use standard crypto • Don’t shared key between devices! • Code integrity, data confidentiality • Restrict and control local access (hardware, …) -
#voxxed_lu #IotSecurityConf What Is Coming? • Lightweight Crypto for the
IoT (LWC) • Software Security • Code security and proof (standard, best practices, formal analysis) • Hardware Security • Side channel-attack and fault-injection • Secure boot and secure firmware update -
#voxxed_lu #IotSecurityConf PACLIDO Protocoles et Algorithmes Cryptographiques Légers pour l’Internet
des Objets Consortium: Airbus, Loria-CNRS, Rtone, Université de Limoge, Trusted Object, Sophia Conseil, CEA Goals: Develop new and IoT compliant crypto primitives and protocols for domotics (BLE), Smart- Cities @fui_paclido paclido.fr -
#voxxed_lu #IotSecurityConf Secure Elements • Tamper resistant hardware • Secure
firmware • Secret keys storage, keys renewal • Crypto. algorithm • Data encryption & decryption -
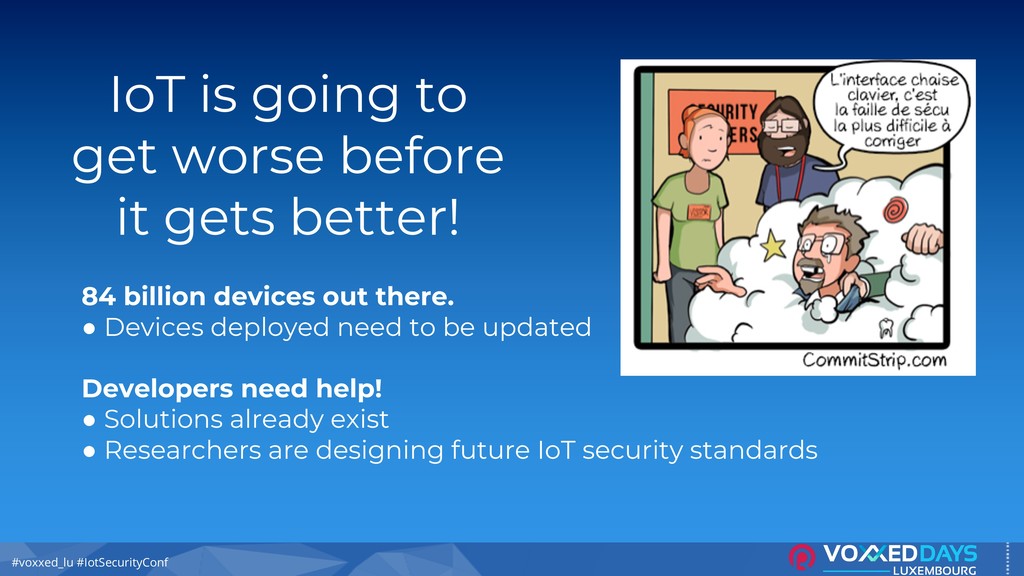
#voxxed_lu #IotSecurityConf IoT is going to get worse before it
gets better! 84 billion devices out there. • Devices deployed need to be updated Developers need help! • Solutions already exist • Researchers are designing future IoT security standards