Share
Embed
Secure Terraform without slowing down developers
Practical DevSecOps guardrails, policy as code, and automated security checks in real CI/CD pipelines.
Amaury Borges Souza
February 18, 2026
Transcript
43 slides
-
© HASHICORP 2 At HashiConf 2025, I met platform engineers,
security leaders, and Terraform practitioners facing the same challenge: How do we secure Terraform without slowing down developers? -
3 Secure Terraform without slowing down developers Practical DevSecOps guardrails,
policy as code, and automated security checks in real CI/CD pipelines. 01 -
4 Hashicorp Ambassador at HashiCorp Hashicorp User Group Lead him/his
@amaurybsouza Amaury Borges Souza 02 -
©2024 HASHICORP 5 Table of Contents The Problem Market Trends
The DevSecOps Mindset Reality in most organizations Terraform features that enable secure delivery Policy as Code Key concepts) 06 07 05 08 10 14 03 -
© HASHICORP 6 The Context: Why This Matters Practical patterns
for secure-by-default Terraform 04 -
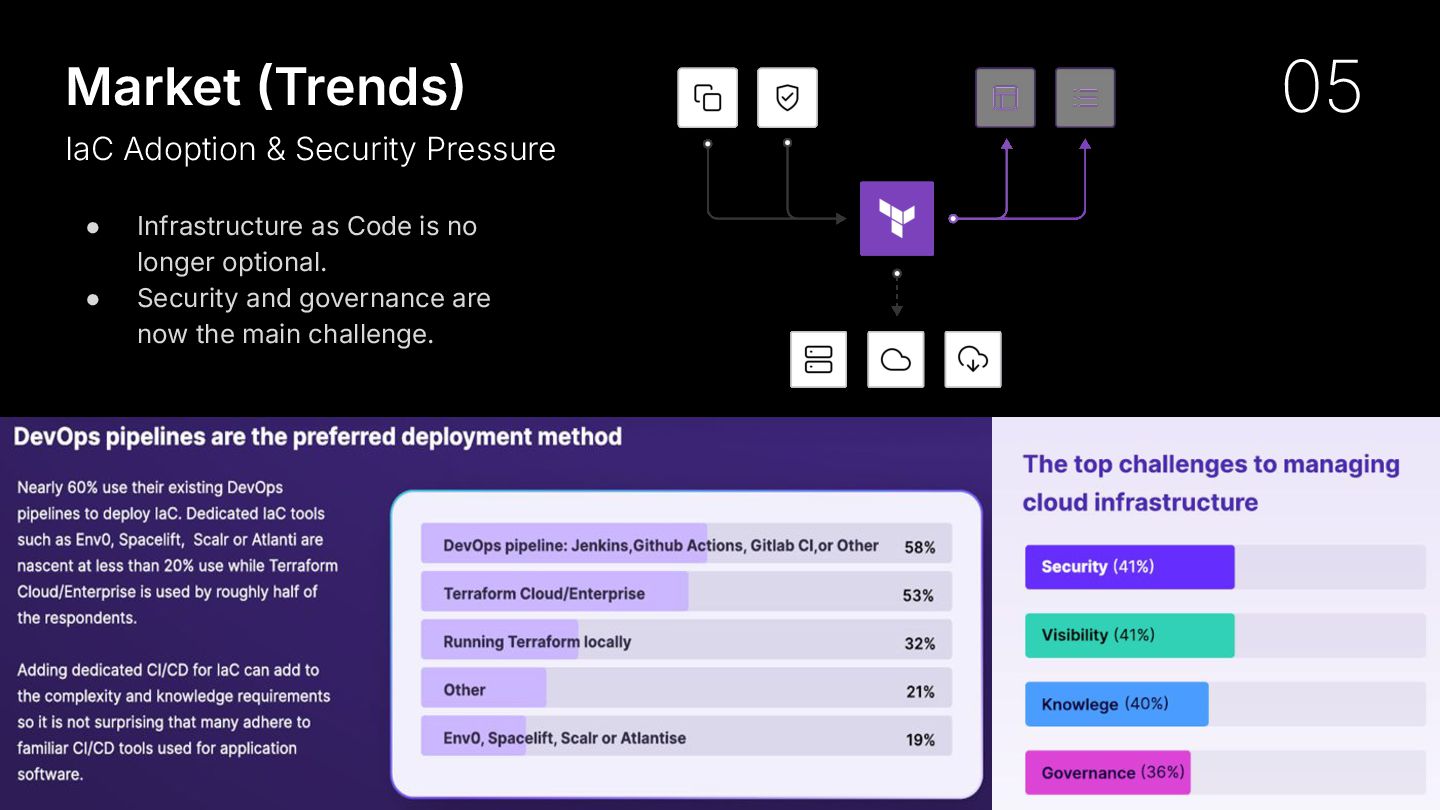
©2024 HASHICORP 7 • Infrastructure as Code is no longer
optional. • Security and governance are now the main challenge. Market Trends IaC Adoption & Security Pressure 05 -
8 The problem 06 Security vs Speed dilemma • Developers
want fast delivery • Security teams want governance and compliance • Manual reviews create bottlenecks • Result: shadow IaC and risky deployments Question: How do we secure Terraform without blocking developers? -
9 Reality in most organizations Security vs Speed dilemma •
Terraform deployed without guardrails • Security checks happen late • Manual approvals slow pipelines • Developers bypass processes Security becomes friction. 07 -
10 The DevSecOps mindset Security must be: • Automated •
Invisible when compliant • Fast • Integrated into developer workflow • Shift-left 08 -
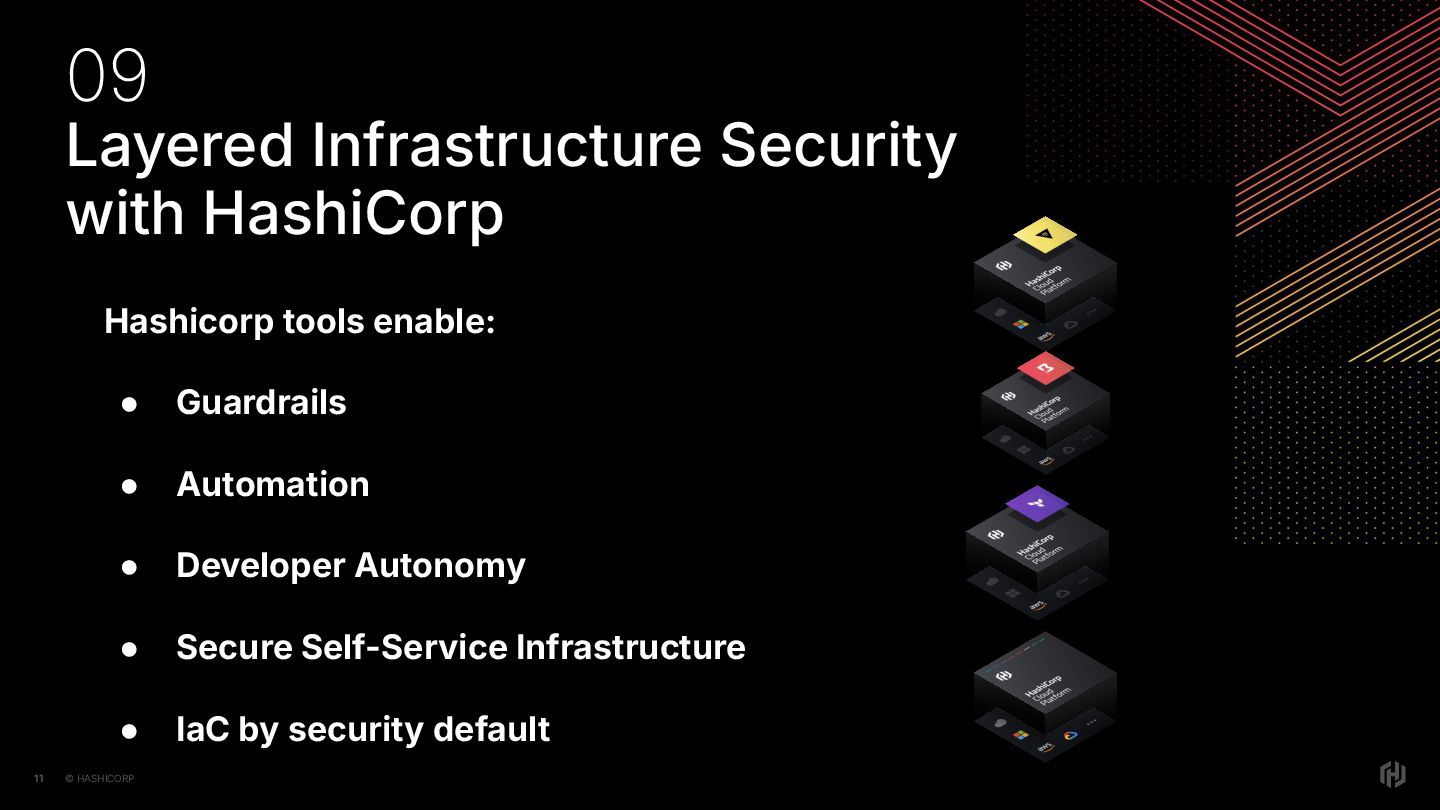
© HASHICORP 11 09 Hashicorp tools enable: • Guardrails •
Automation • Developer Autonomy • Secure Self-Service Infrastructure • IaC by security default Layered Infrastructure Security with HashiCorp -
©2024 HASHICORP 10 12 Terraform features that enable secure delivery
Terraform capabilities that help security and governance: • Plan & Apply workflow • Reusable Modules • State management • Validation & formatting (validate / fmt) • Actions & automation -
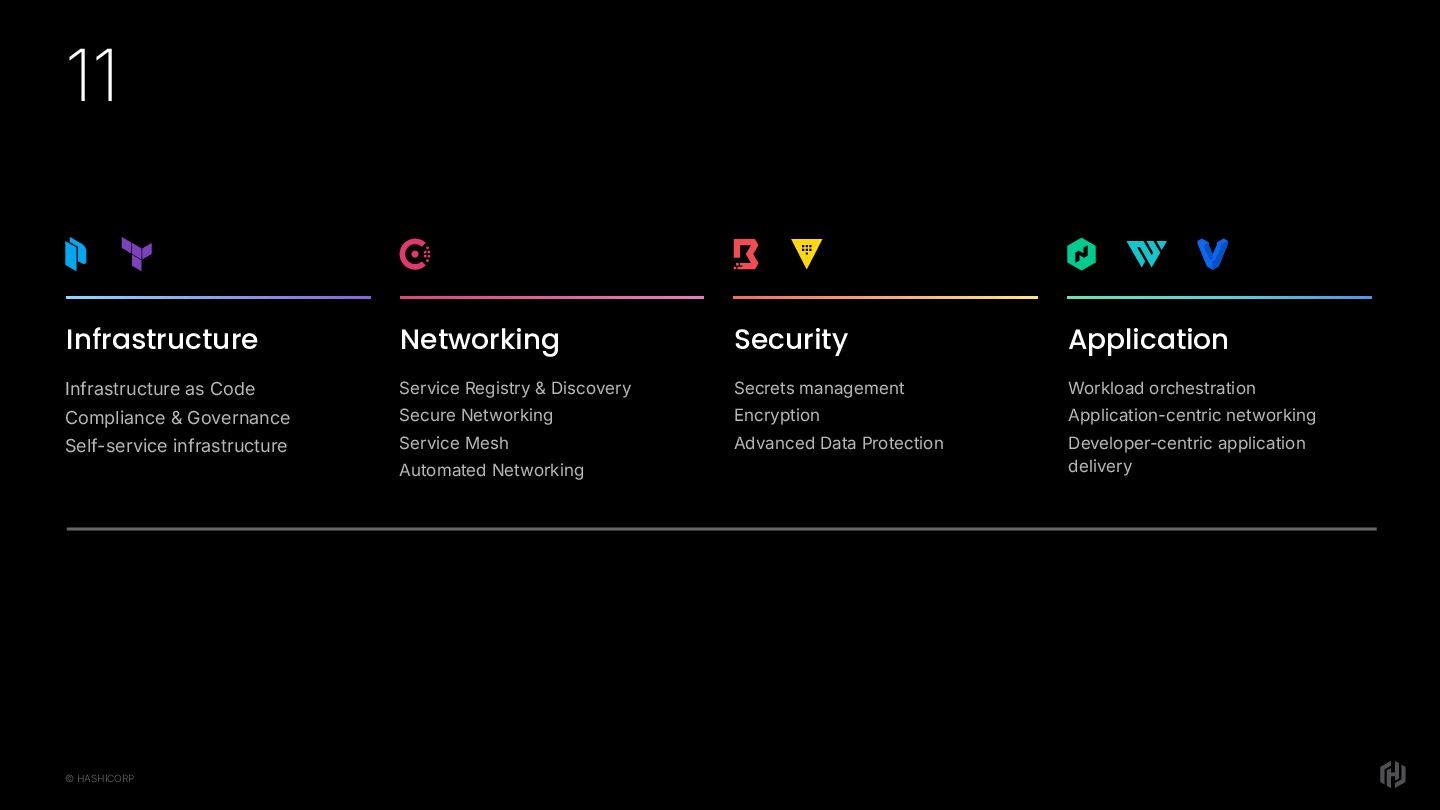
© HASHICORP Infrastructure Networking Security Application Infrastructure as Code Compliance
& Governance Self-service infrastructure Service Registry & Discovery Secure Networking Service Mesh Automated Networking Secrets management Encryption Advanced Data Protection Workload orchestration Application-centric networking Developer-centric application delivery 11 -
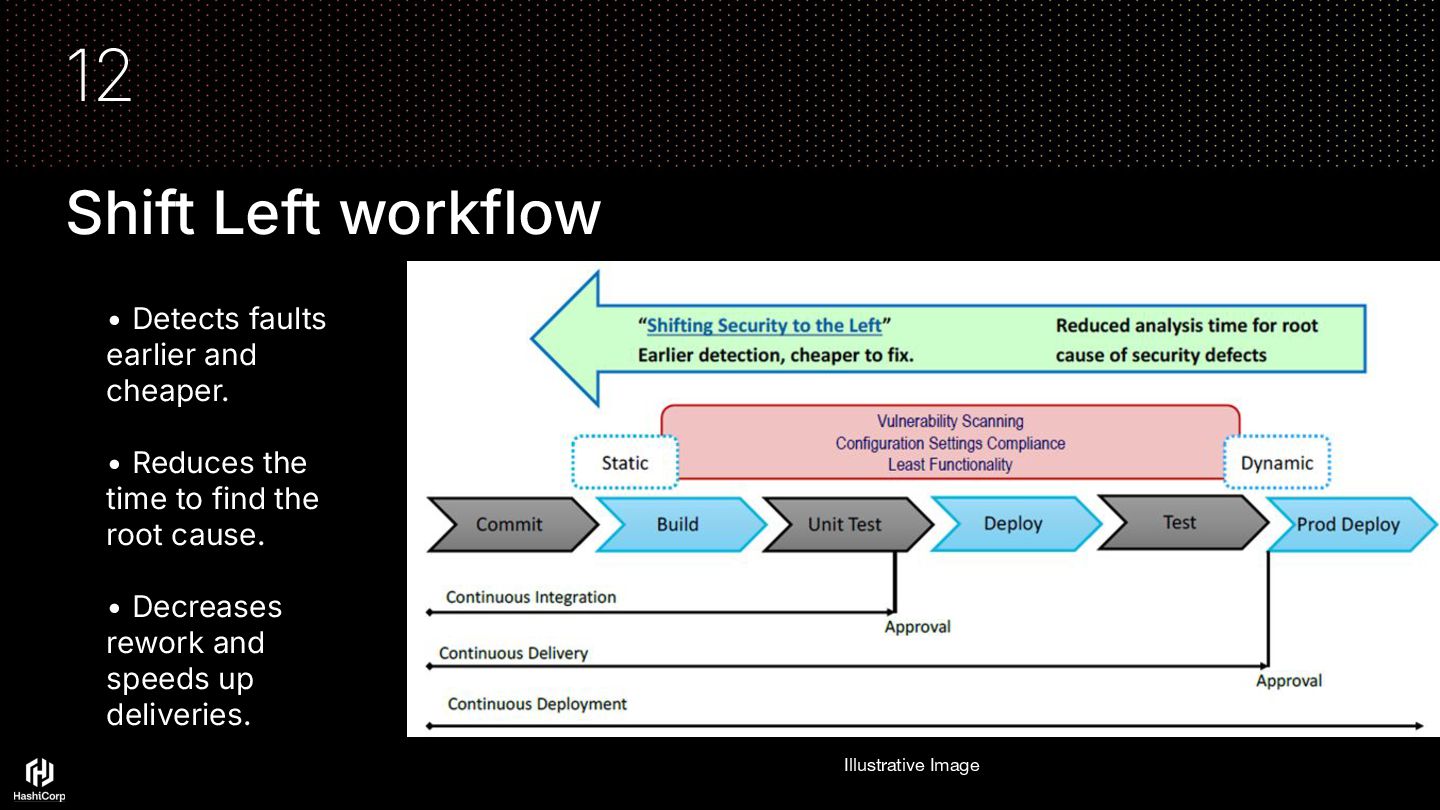
14 Shift Left workflow • Detects faults earlier and cheaper.
• Reduces the time to find the root cause. • Decreases rework and speeds up deliveries. 12 Illustrative Image -
© HASHICORP 15 Policy as Code turns governance rules into
executable logic. Fast, predictable feedback 13 -
16 Policy as Code Key concepts) Guardrails instead of gates:
• Define policy once • Enforce automatically • Developers get immediate feedback • No manual security tickets Security becomes predictable and scalable 14 -
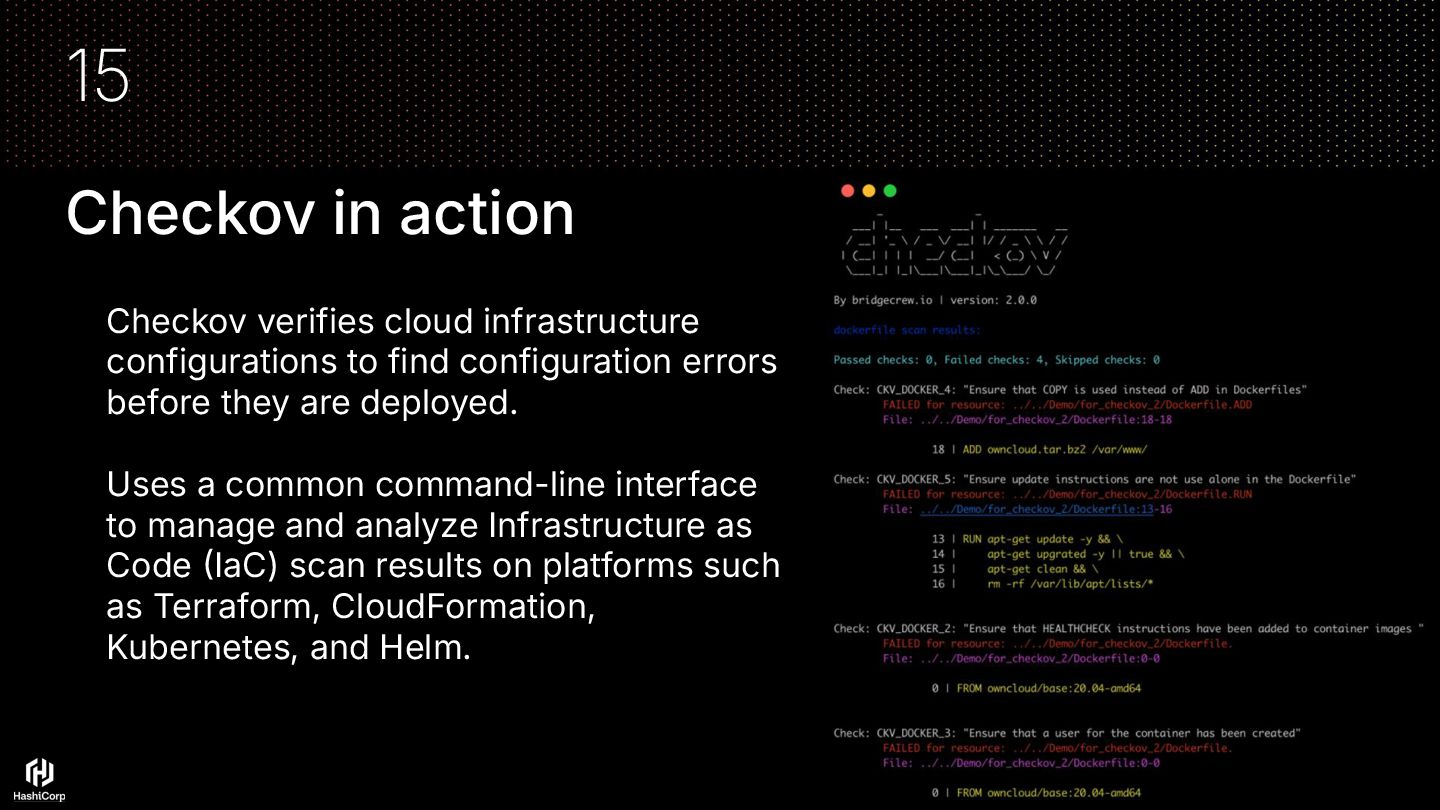
17 Checkov in action Checkov verifies cloud infrastructure configurations to
find configuration errors before they are deployed. Uses a common command-line interface to manage and analyze Infrastructure as Code IaC) scan results on platforms such as Terraform, CloudFormation, Kubernetes, and Helm. 15 -
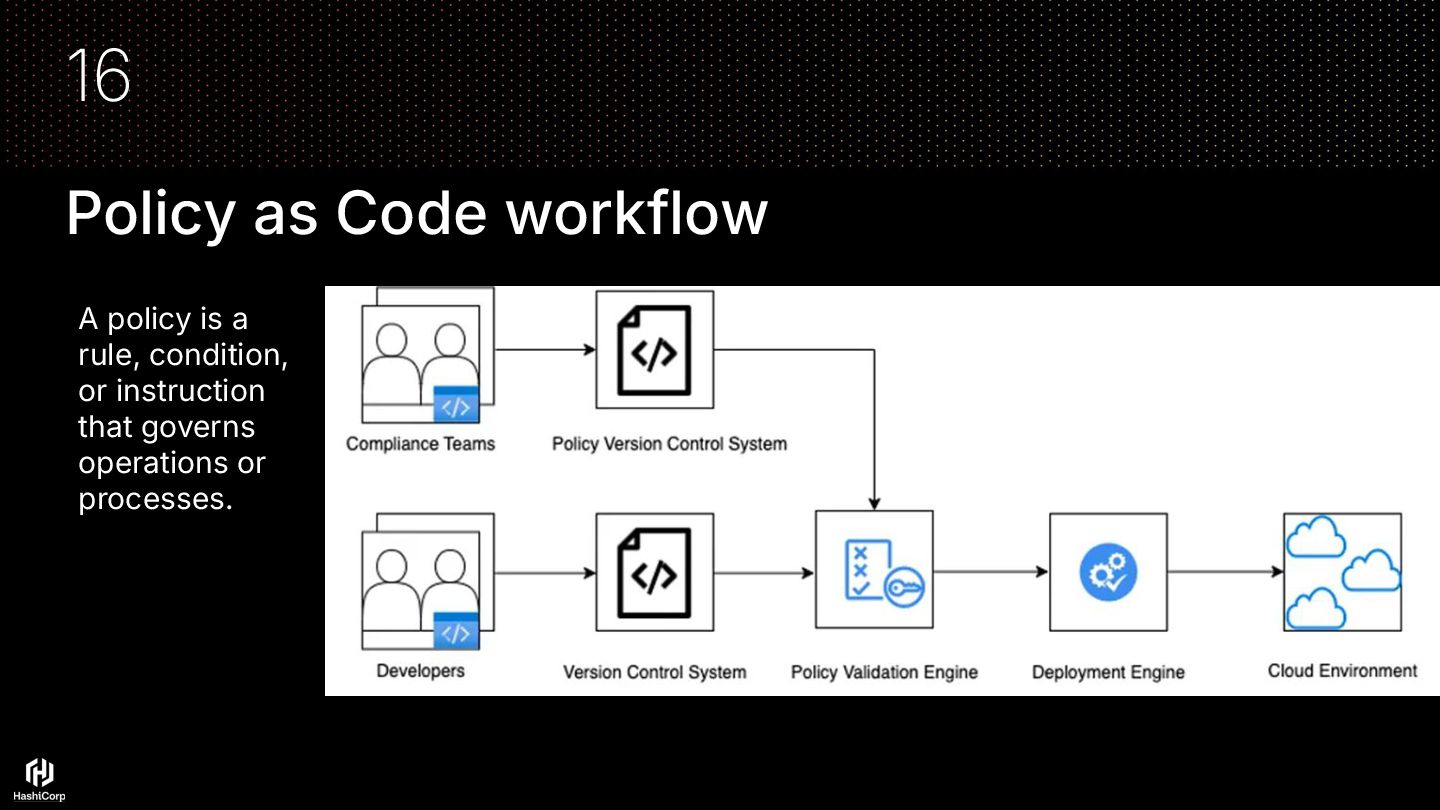
18 Policy as Code workflow 16 A policy is a
rule, condition, or instruction that governs operations or processes. -
©2024 HASHICORP Hashicorp Sentinel Policy as Code engine integrated with
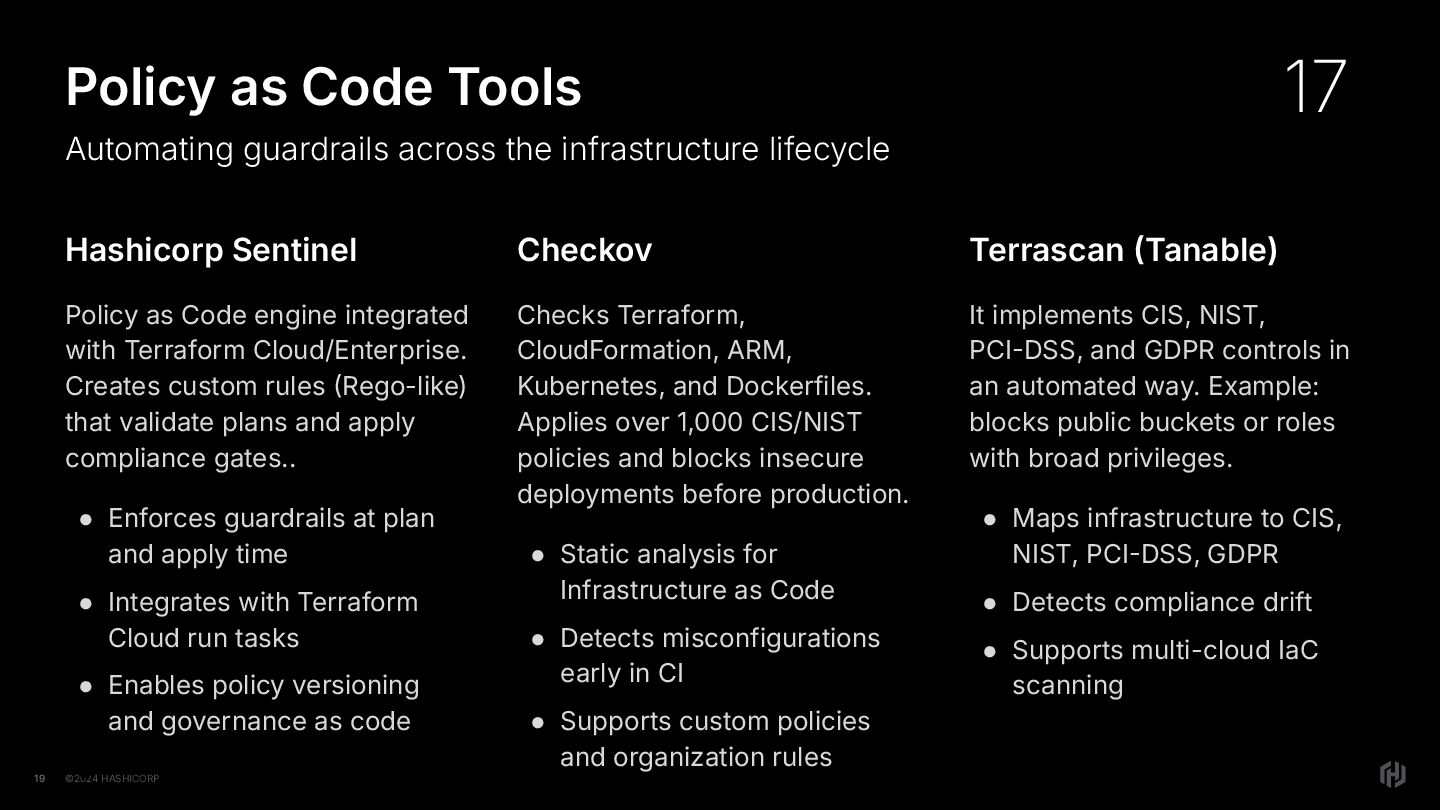
Terraform Cloud/Enterprise. Creates custom rules Rego-like) that validate plans and apply compliance gates.. • Enforces guardrails at plan and apply time • Integrates with Terraform Cloud run tasks • Enables policy versioning and governance as code • 19 Policy as Code Tools Automating guardrails across the infrastructure lifecycle Checkov Checks Terraform, CloudFormation, ARM, Kubernetes, and Dockerfiles. Applies over 1,000 CIS/NIST policies and blocks insecure deployments before production. • Static analysis for Infrastructure as Code • Detects misconfigurations early in CI • Supports custom policies and organization rules Terrascan Tanable) It implements CIS, NIST, PCIDSS, and GDPR controls in an automated way. Example: blocks public buckets or roles with broad privileges. • Maps infrastructure to CIS, NIST, PCIDSS, GDPR • Detects compliance drift • Supports multi-cloud IaC scanning 17 -
© HASHICORP 20 Infrastructure Risk in CI/CD Plans are not
validated, IAM is not reviewed, state is exposed 18 -
21 Real Failure Stories Hereʼs what happens when security is
bolted on later. • Exposed S3 bucket • Over-permissive IAM role • Hardcoded secrets 19 -
22 Publicly Exposed Terraform State File Additional Real Failure Scenarios
Dev-Focused). • State file stored in public S3 • Credentials leaked via state • Lateral movement across environments 20 -
23 Runtime vs Plan-Time Security • Plan-time Checkov, Sentinel) •
Apply-time enforcement • Runtime monitoring CSPM / CWPP Prevention is not enough without visibility. 21 -
© HASHICORP 24 Secure Pipeline in Practice Real-world pipeline patterns
and the tools that enable secure Terraform delivery. 22 -
©2024 HASHICORP 25 Checkov An open-source tool developed by Bridgecrew
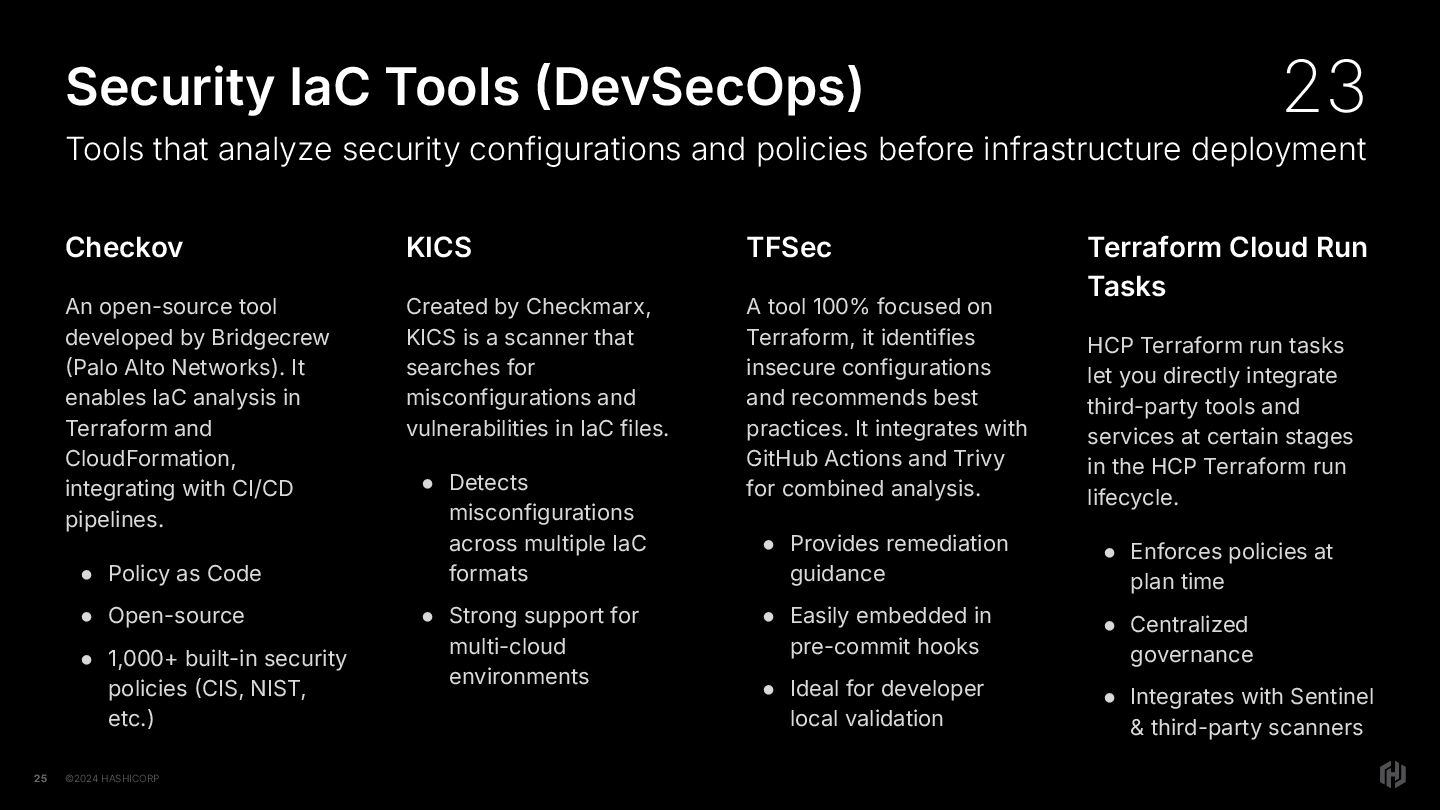
Palo Alto Networks). It enables IaC analysis in Terraform and CloudFormation, integrating with CI/CD pipelines. • Policy as Code • Open-source • 1,000+ built-in security policies CIS, NIST, etc.) 25 Tools that analyze security configurations and policies before infrastructure deployment KICS Created by Checkmarx, KICS is a scanner that searches for misconfigurations and vulnerabilities in IaC files. • Detects misconfigurations across multiple IaC formats • Strong support for multi-cloud environments TFSec A tool 100% focused on Terraform, it identifies insecure configurations and recommends best practices. It integrates with GitHub Actions and Trivy for combined analysis. • Provides remediation guidance • Easily embedded in pre-commit hooks • Ideal for developer local validation Terraform Cloud Run Tasks HCP Terraform run tasks let you directly integrate third-party tools and services at certain stages in the HCP Terraform run lifecycle. • Enforces policies at plan time • Centralized governance • Integrates with Sentinel & third-party scanners Security IaC Tools DevSecOps) 23 -
26 Key Principles Secure Terraform without friction: • Automate everything
• Shift-Left security • Provide fast feedback • Use policy as code 24 -
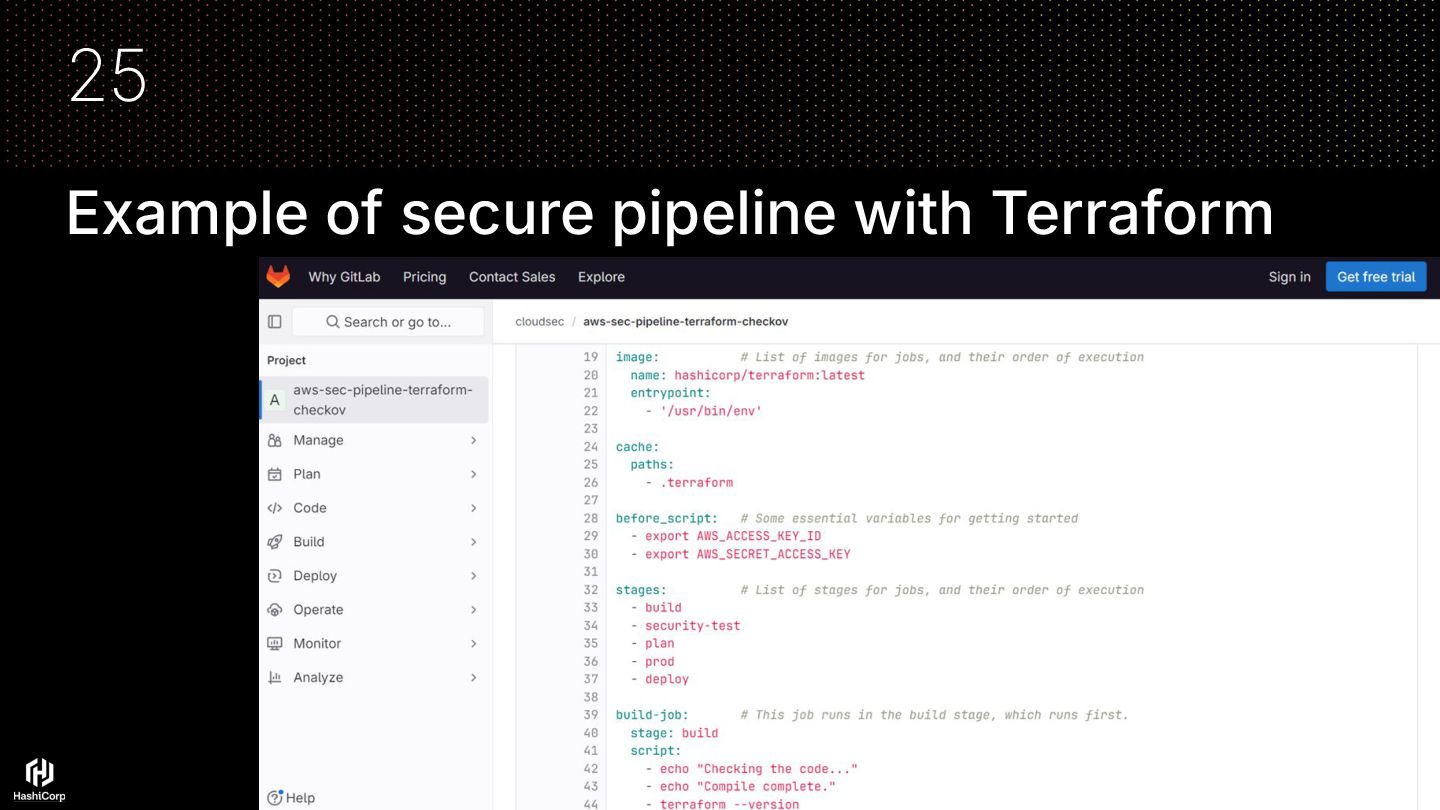
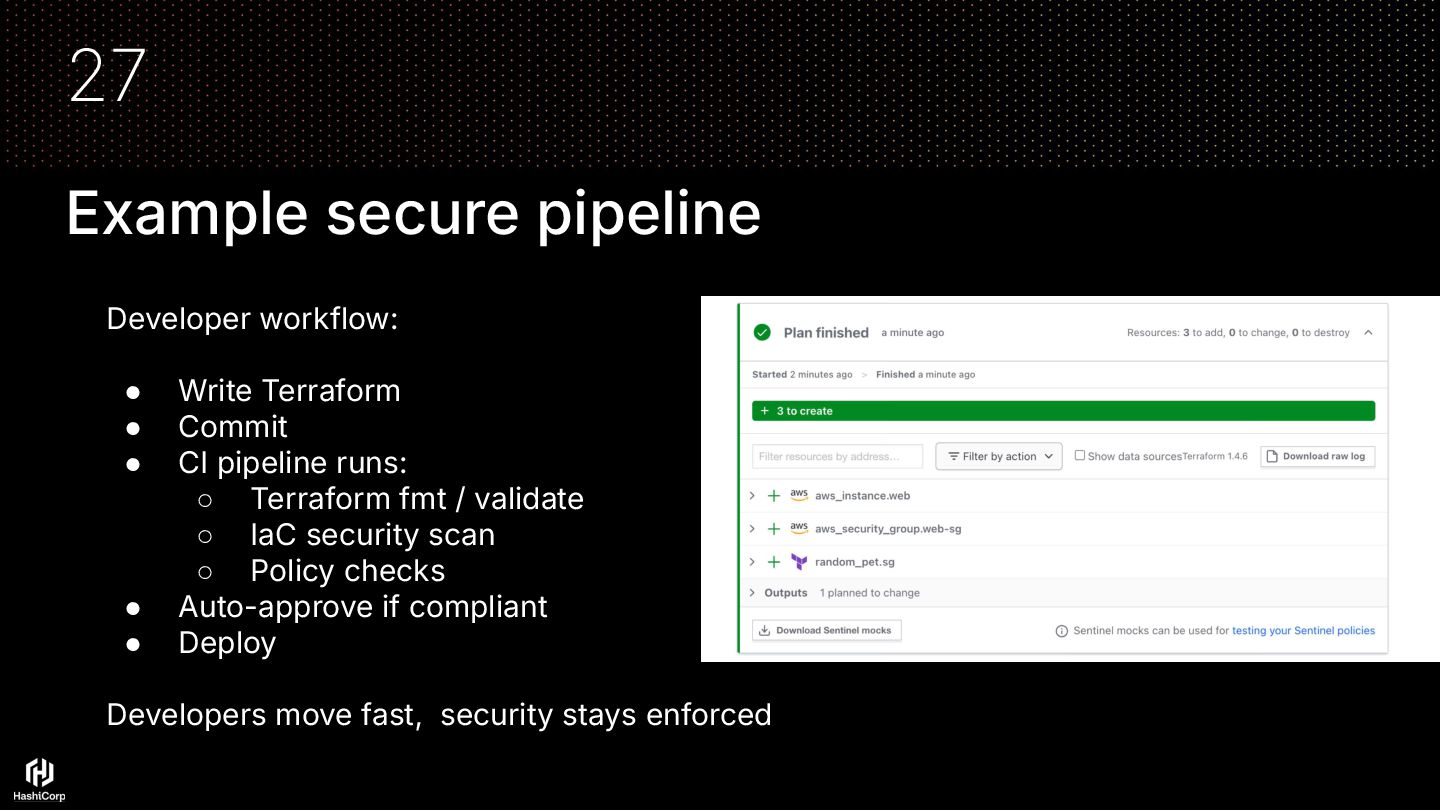
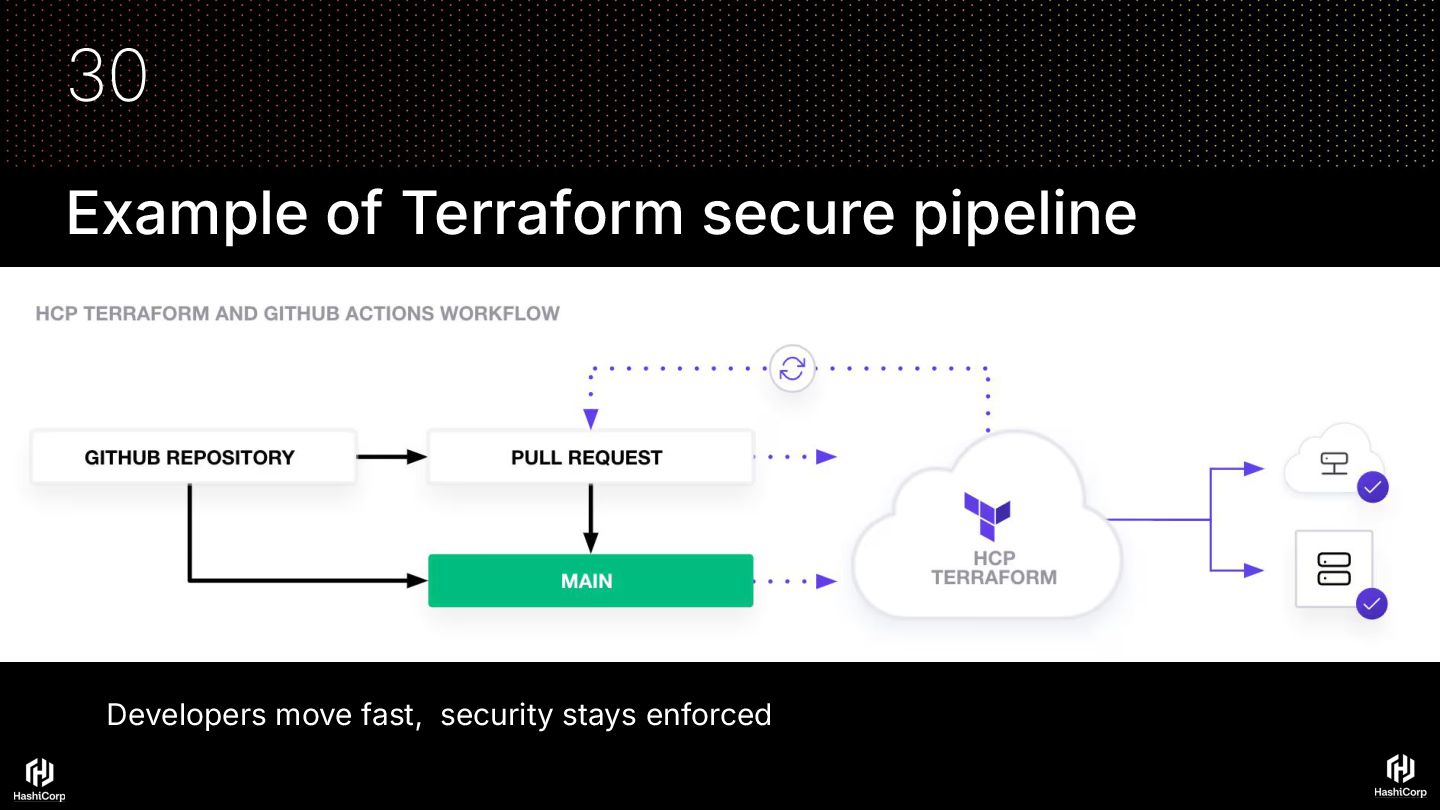
29 Example secure pipeline Developer workflow: • Write Terraform •
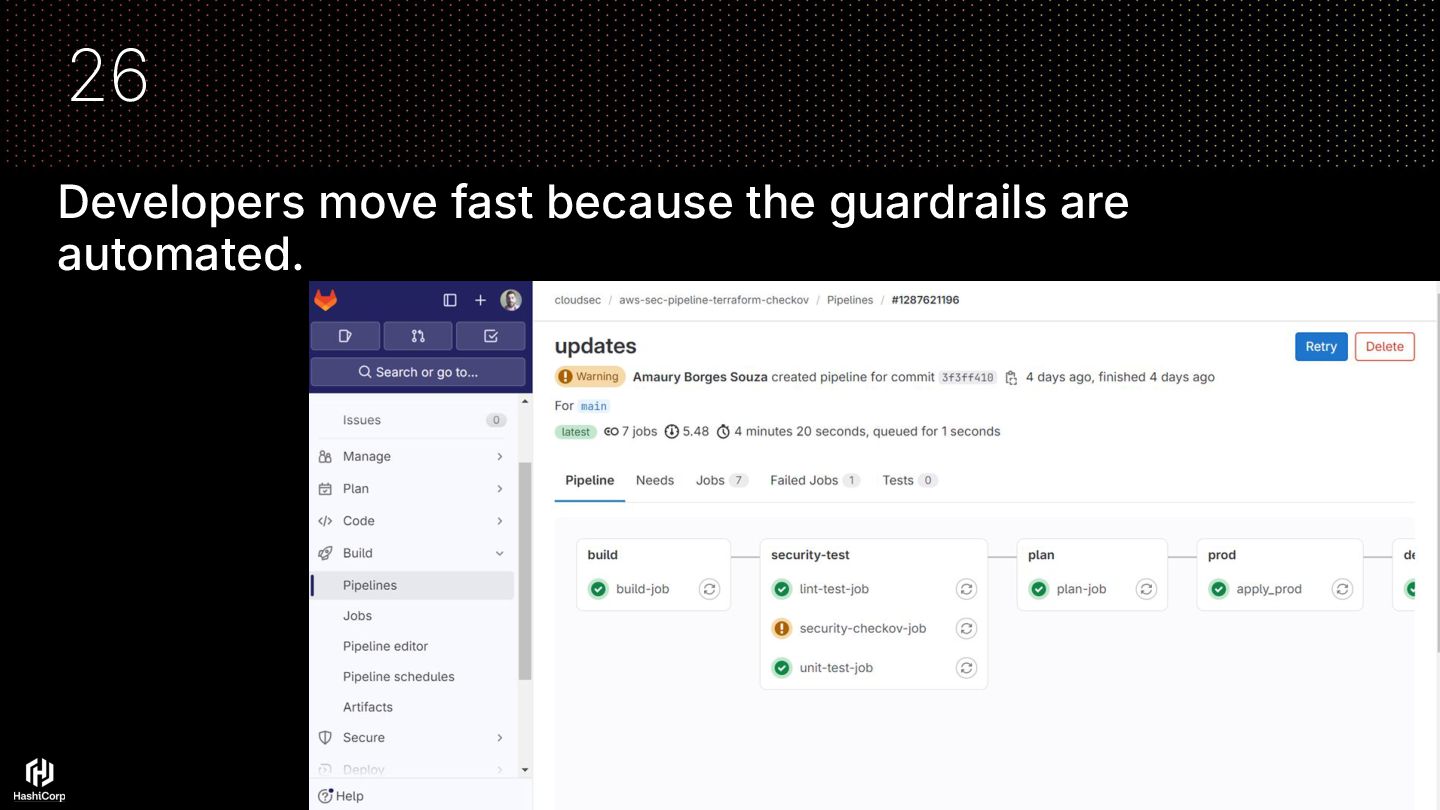
Commit • CI pipeline runs: ◦ Terraform fmt / validate ◦ IaC security scan ◦ Policy checks • Auto-approve if compliant • Deploy Developers move fast, security stays enforced 27 -
30 Security should not block developers unnecessarily Implementation strategy: •
Soft fail for Medium issues • Hard fail only for Critical findings • Direct feedback in Pull Requests 28 -
31 Explicit Terraform Validation & Formatting These steps ensure: •
Consistent code formatting across teams • Early detection of syntax and configuration errors • Reduced review friction • Higher confidence before plan and apply This reflects a production-grade Terraform workflow. 29 -
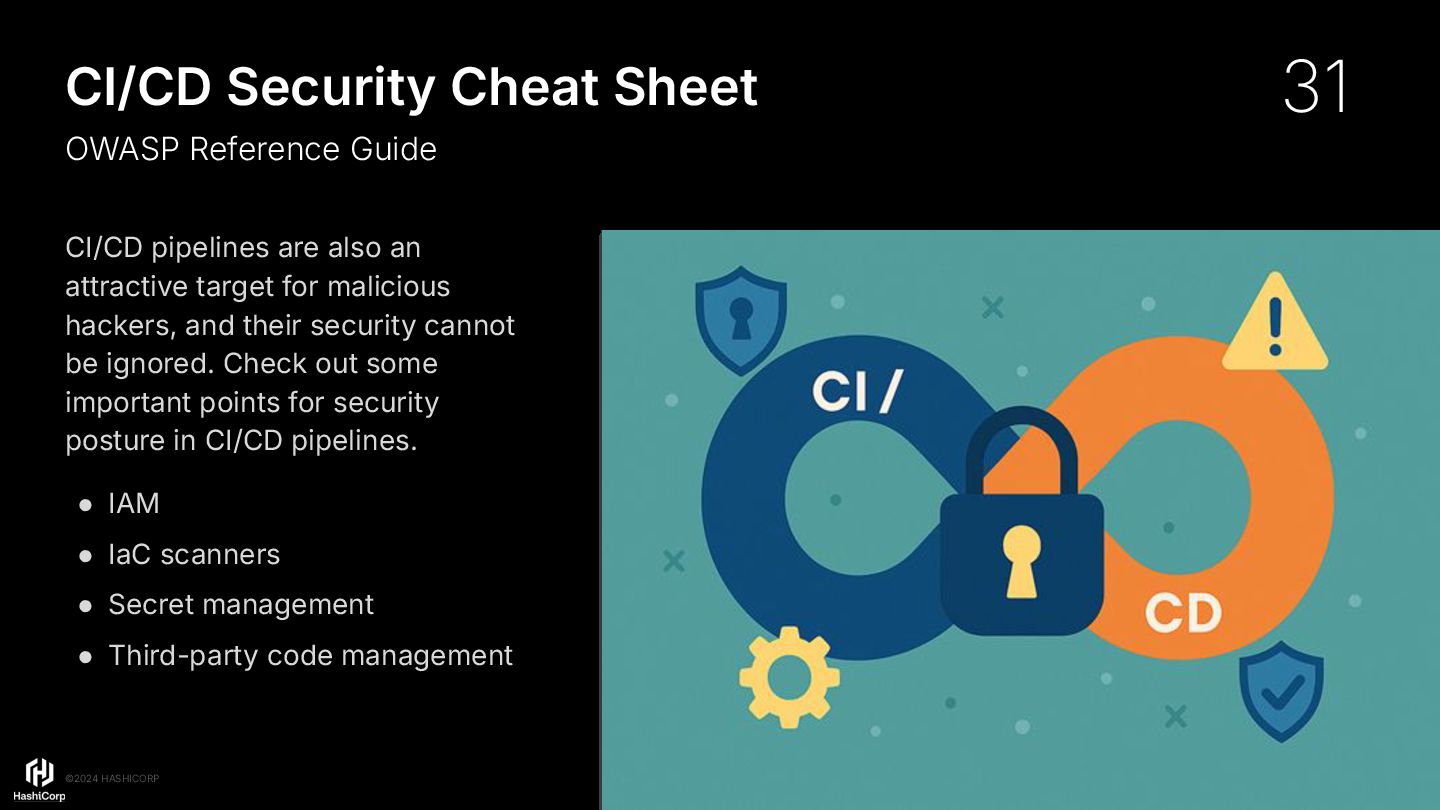
©2024 HASHICORP 32 CI/CD pipelines are also an attractive target
for malicious hackers, and their security cannot be ignored. Check out some important points for security posture in CI/CD pipelines. • IAM • IaC scanners • Secret management • Third-party code management CI/CD Security Cheat Sheet OWASP Reference Guide 31 -
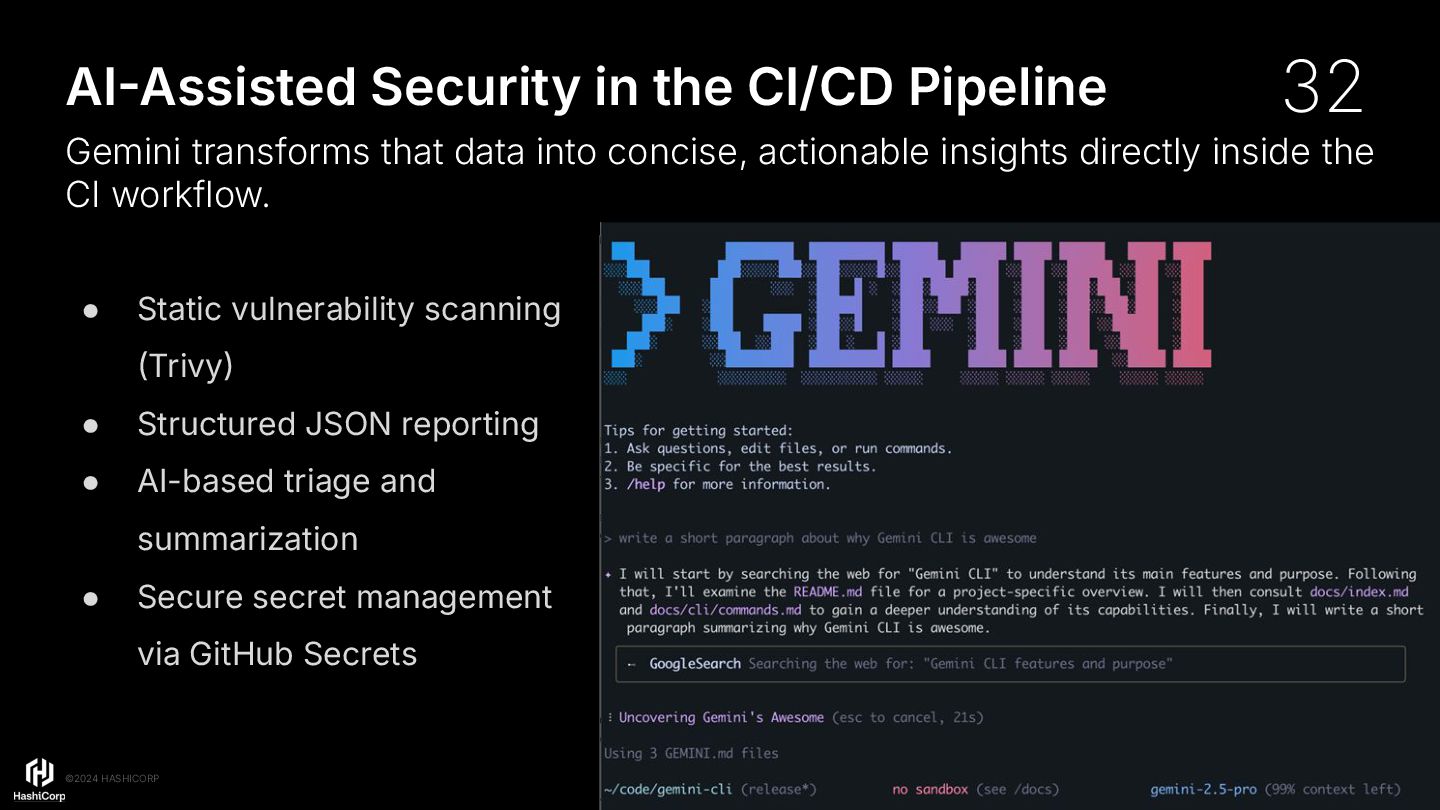
©2024 HASHICORP 33 • Static vulnerability scanning Trivy • Structured
JSON reporting • AI-based triage and summarization • Secure secret management via GitHub Secrets AIAssisted Security in the CI/CD Pipeline Gemini transforms that data into concise, actionable insights directly inside the CI workflow. 32 -
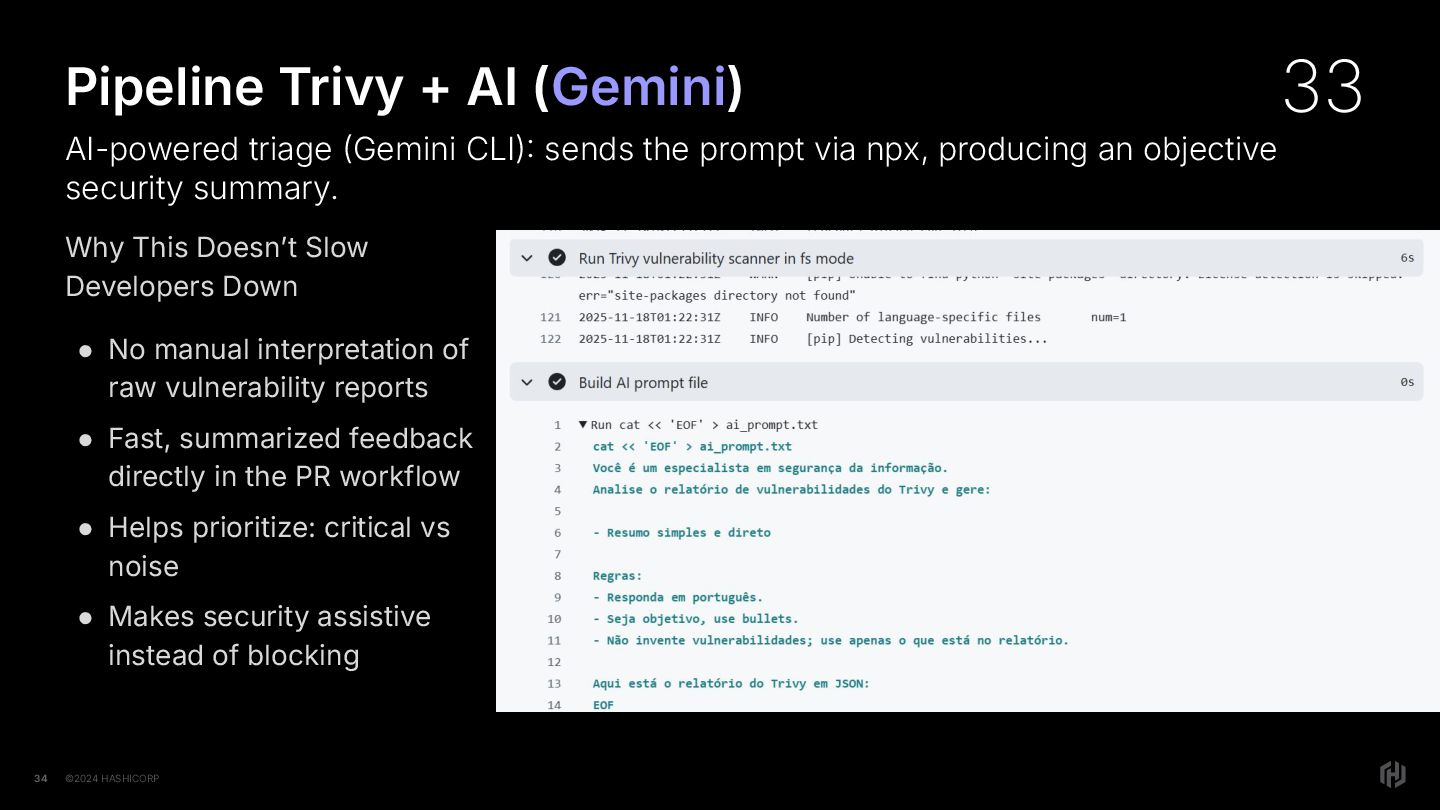
©2024 HASHICORP 34 Why This Doesnʼt Slow Developers Down •
No manual interpretation of raw vulnerability reports • Fast, summarized feedback directly in the PR workflow • Helps prioritize: critical vs noise • Makes security assistive instead of blocking Pipeline Trivy + AI (Gemini) AI-powered triage Gemini CLI sends the prompt via npx, producing an objective security summary. 33 -
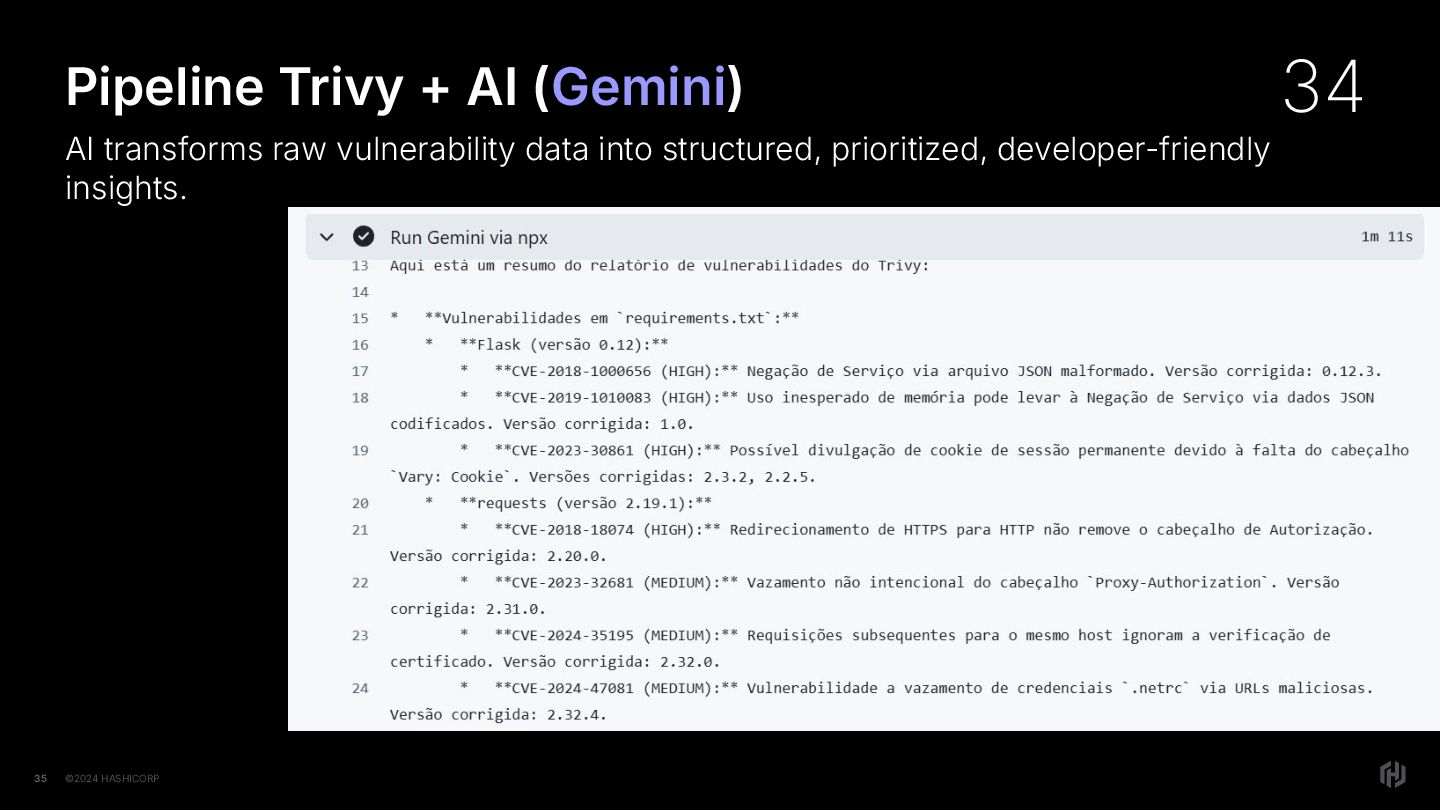
©2024 HASHICORP 35 Pipeline Trivy + AI (Gemini) AI transforms
raw vulnerability data into structured, prioritized, developer-friendly insights. 34 -
36 Terraform Security Checklist for Developers • Run terraform fmt
and validate • Scan with Checkov / Trivy / Terrascan • Enforce policy as code Sentinel / OPA • Define soft vs hard fail strategy • Use Vault or cloud secret managers 35 Security Secrets management Encryption Advanced Data Protection Infrastructure Infrastructure as Code Compliance & Governance Self-service infrastructure -
37 Questions? • What is the real risk of leaving
security until the end of development? • What are the real risks of applying IaC without static validation and analysis tools Checkov, TFLint, tfsec, etc.? 37 -
© HASHICORP 38 HashiCorp User Group Campinas now on LinkedIn
We host technical meetups, hands-on sessions, and community discussions focused on building secure, scalable cloud platforms. Everyone is welcome to join and contribute. 36 -
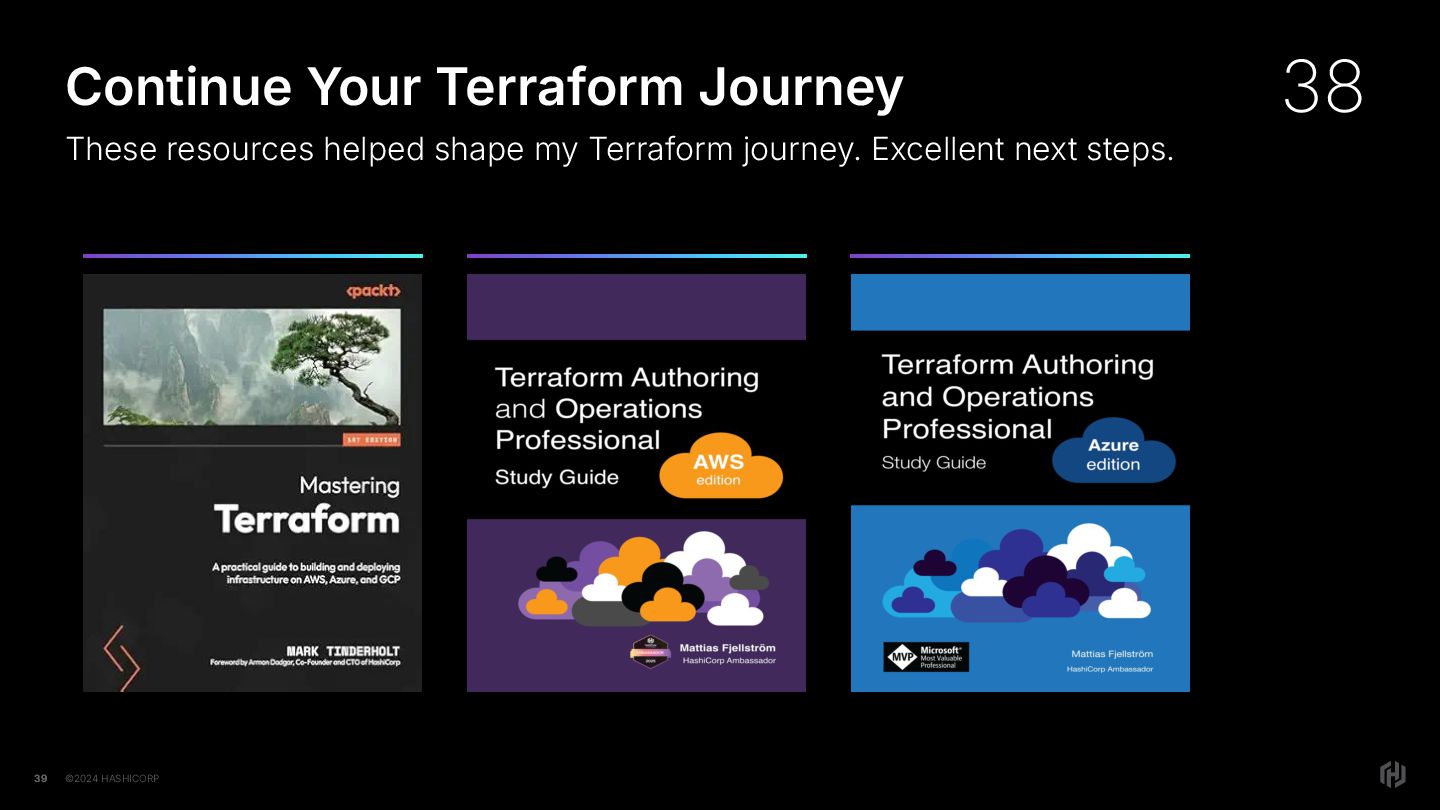
©2024 HASHICORP 39 39 Continue Your Terraform Journey These resources
helped shape my Terraform journey. Excellent next steps. 38 -
41 Terraform features that enable secure delivery Terraform capabilities that
help security and governance: • Plan & Apply workflow • Reusable Modules • State management • Validation & formatting (validate / fmt) • Actions & automation 06 -
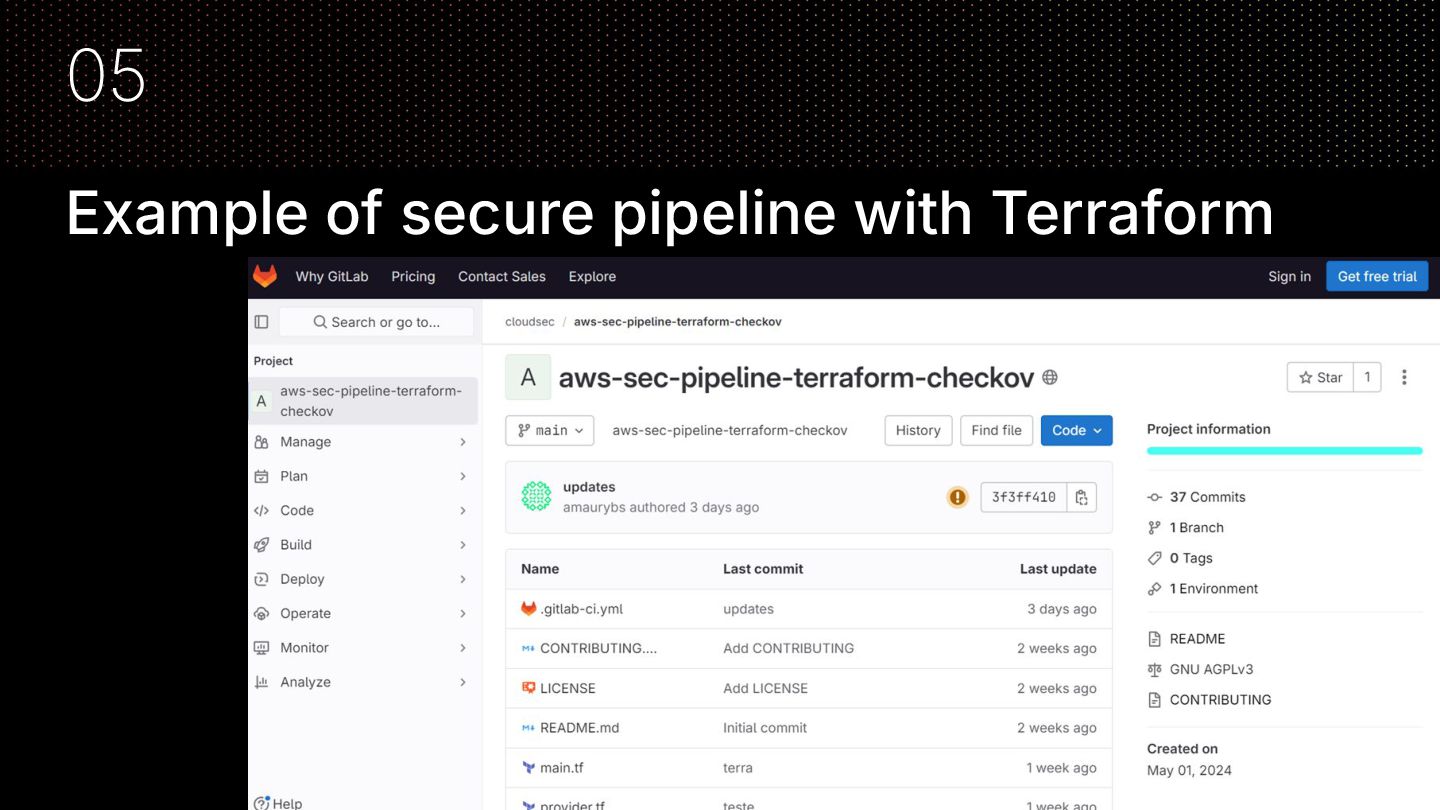
43 Example of Terraform secure pipeline Developer workflow: • Write
Terraform • Commit • CI pipeline runs: ◦ Terraform fmt / validate ◦ IaC security scan ◦ Policy checks • Auto-approve if compliant • Deploy Developers move fast, security stays enforced 30