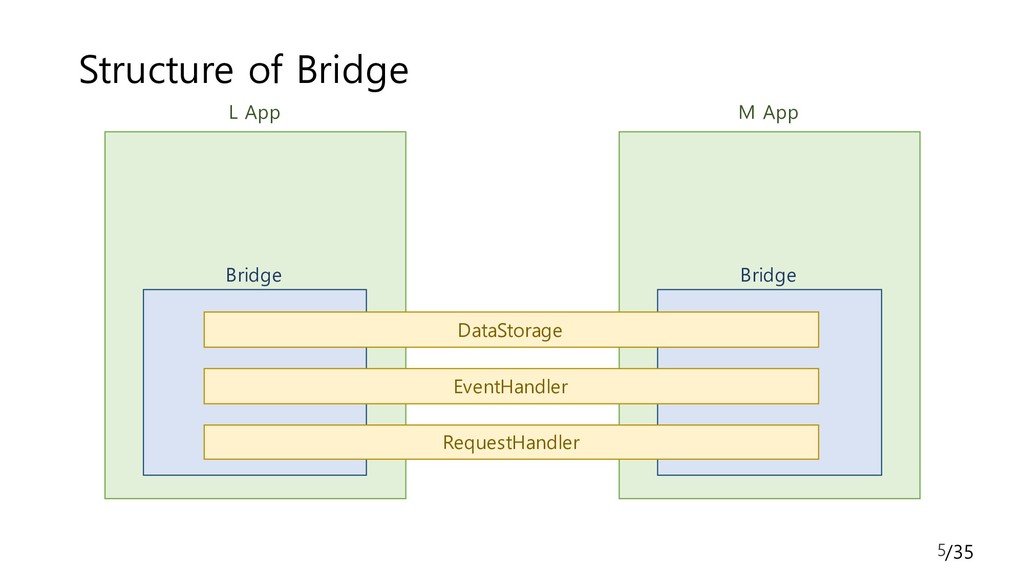
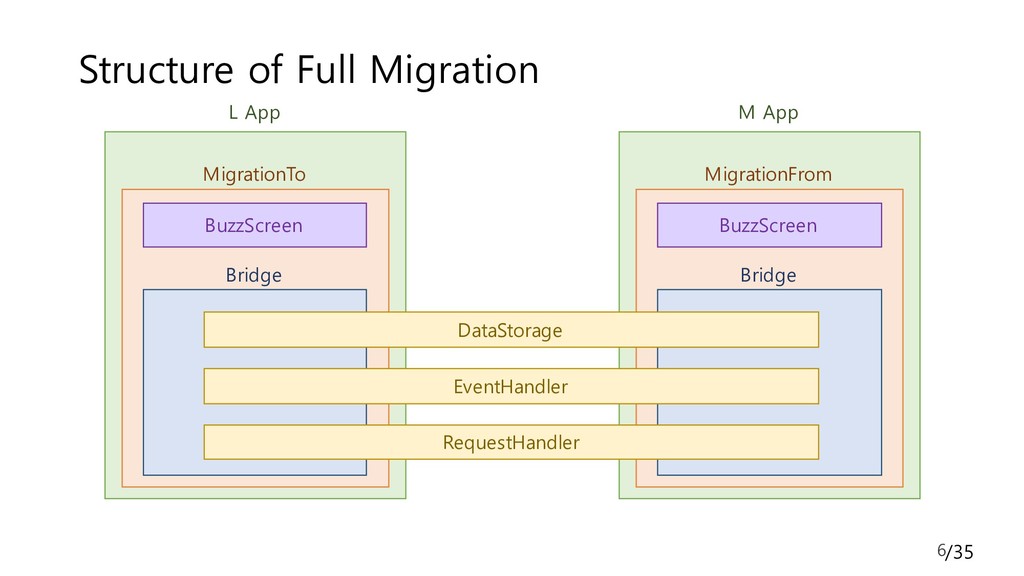
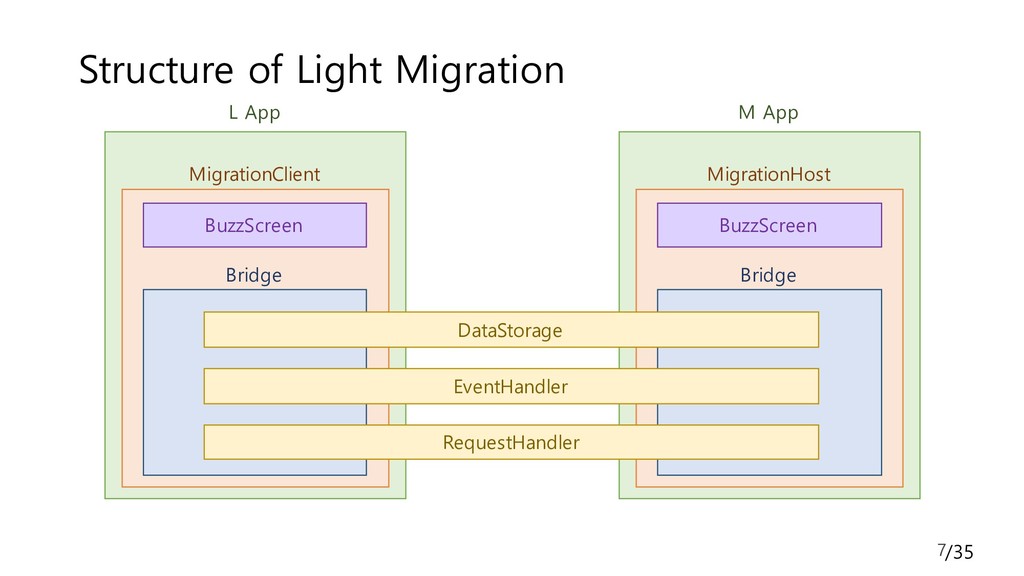
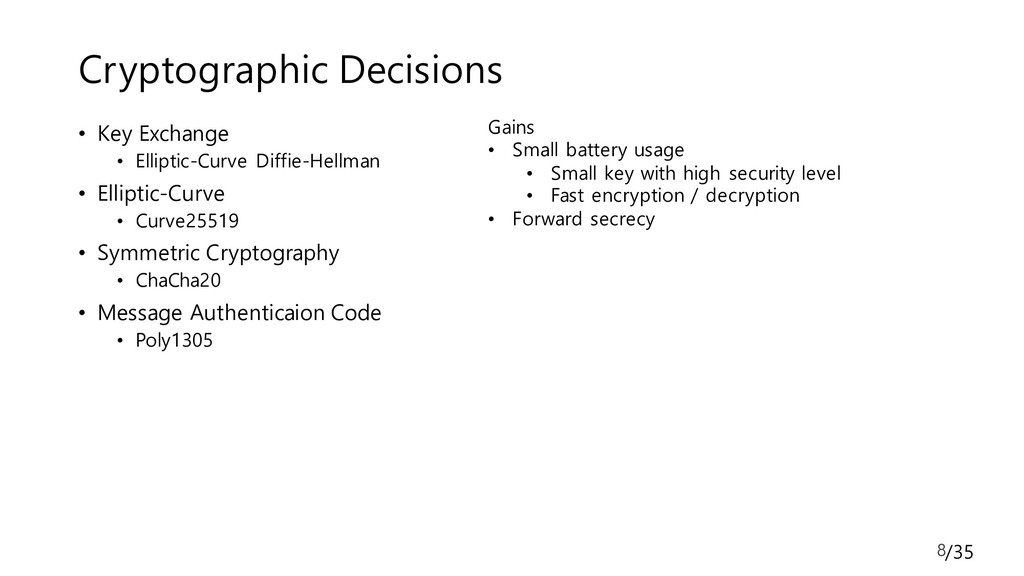
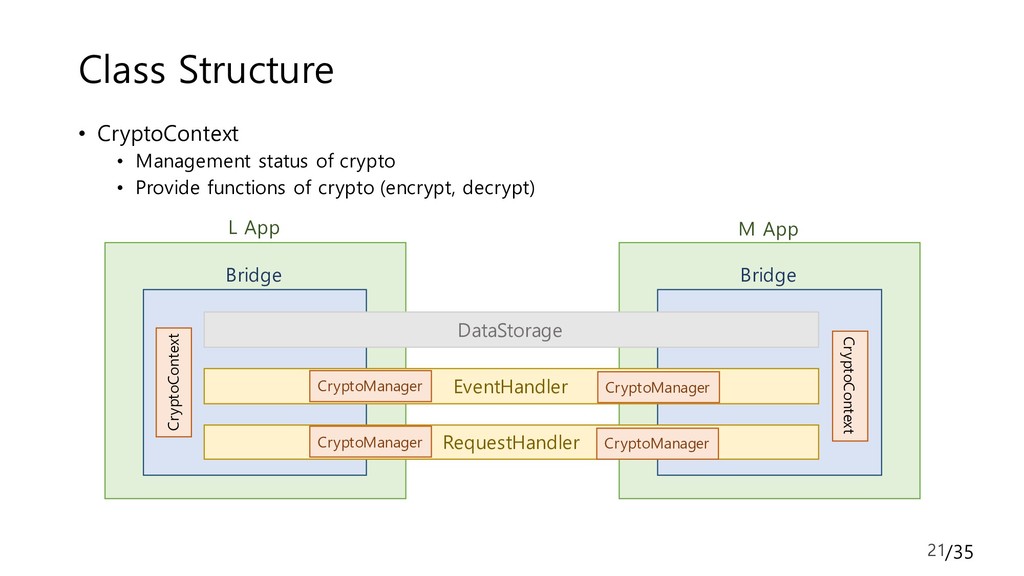
Bridge • Cryptographic Part • Cryptographic Decision: ECDH with Curve25519, ChaCha20-Poly1305 • Study of cryptography • Implementation Part • Library • Class Structure • Handshake • Flows • Remain Works 3
between M app and L app on the bridge • Problems • Save the secret key in the source code? • If use asymmetric cipher, then how handle the handshake • If a message is lost… • If both start handshake at the same time • If the session key is lost… • Hard to reproduce corner cases of the parallel processing • If encryption is failed, the communication is blocked • If once it released, can we change the handshake algorithm compatible with older one? • ….. • Need your help! 4
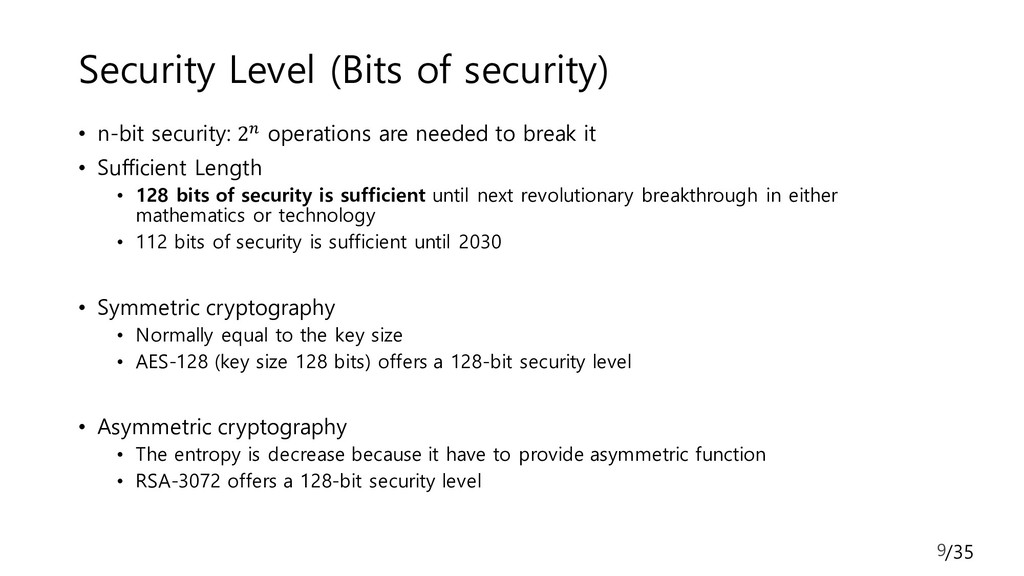
operations are needed to break it • Sufficient Length • 128 bits of security is sufficient until next revolutionary breakthrough in either mathematics or technology • 112 bits of security is sufficient until 2030 • Symmetric cryptography • Normally equal to the key size • AES-128 (key size 128 bits) offers a 128-bit security level • Asymmetric cryptography • The entropy is decrease because it have to provide asymmetric function • RSA-3072 offers a 128-bit security level 9
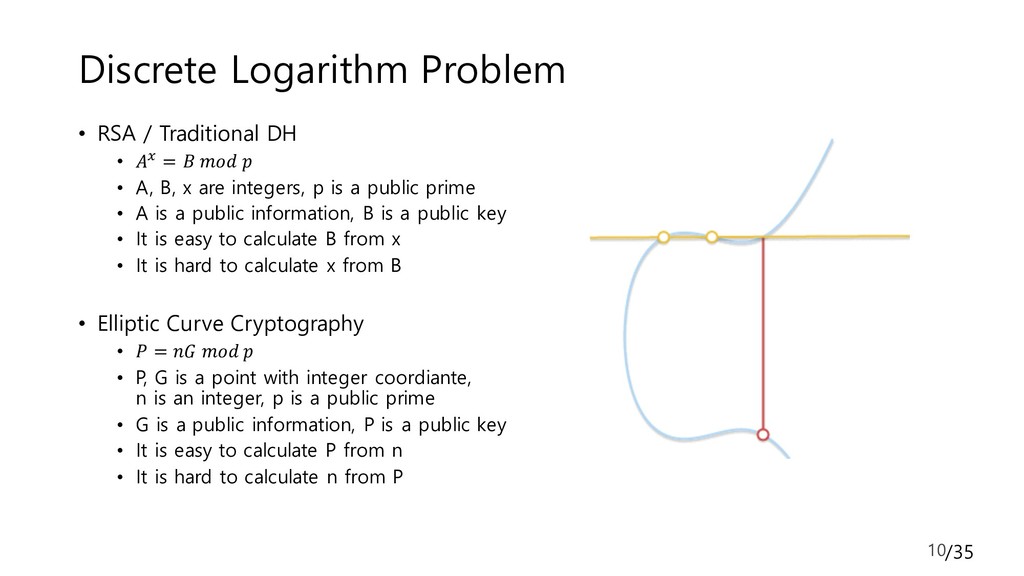
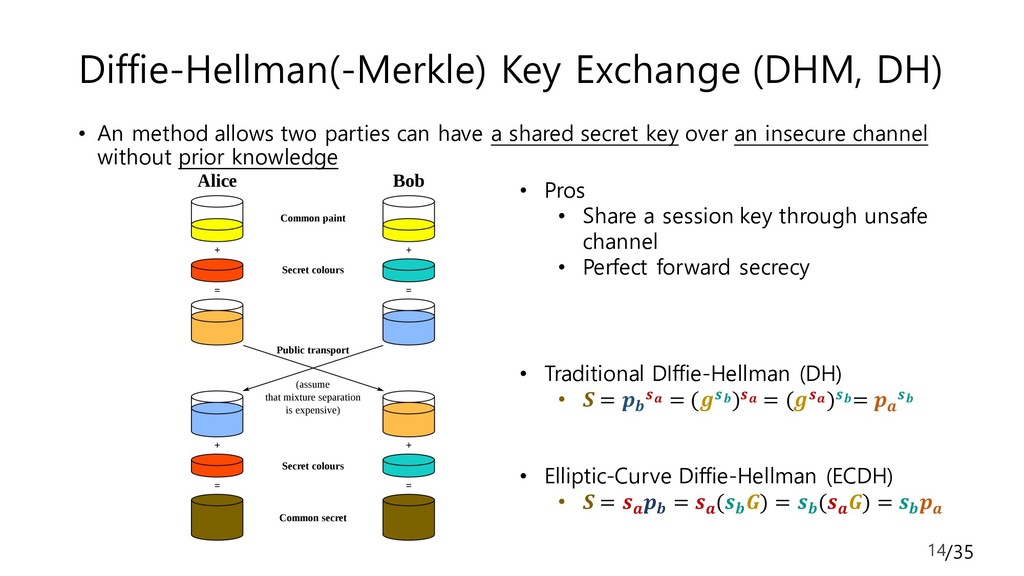
$ = • A, B, x are integers, p is a public prime • A is a public information, B is a public key • It is easy to calculate B from x • It is hard to calculate x from B • Elliptic Curve Cryptography • = • P, G is a point with integer coordiante, n is an integer, p is a public prime • G is a public information, P is a public key • It is easy to calculate P from n • It is hard to calculate n from P 10
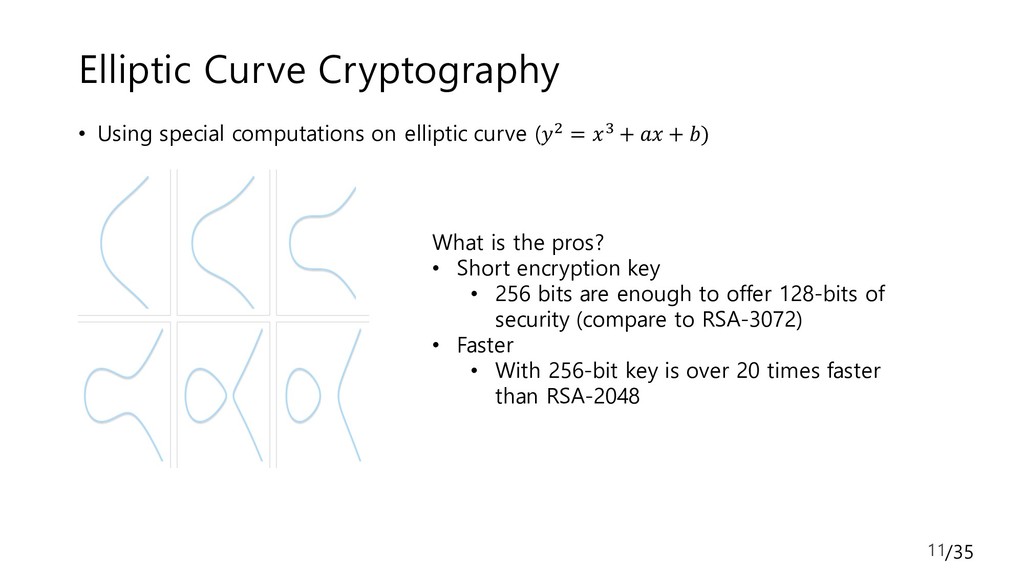
curve (0 = 2 + + ) What is the pros? • Short encryption key • 256 bits are enough to offer 128-bits of security (compare to RSA-3072) • Faster • With 256-bit key is over 20 times faster than RSA-2048 11
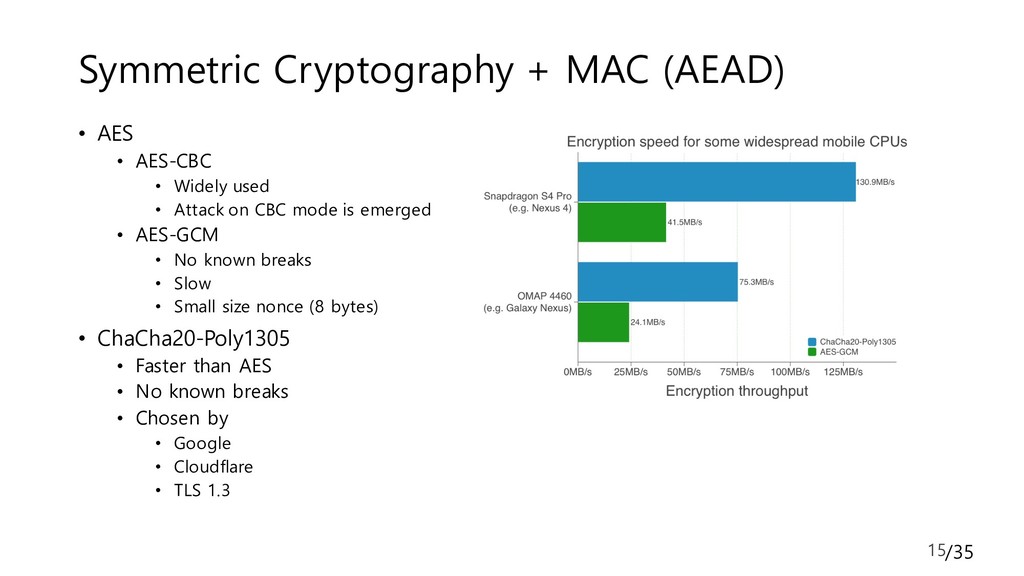
• Widely used • Attack on CBC mode is emerged • AES-GCM • No known breaks • Slow • Small size nonce (8 bytes) • ChaCha20-Poly1305 • Faster than AES • No known breaks • Chosen by • Google • Cloudflare • TLS 1.3 15
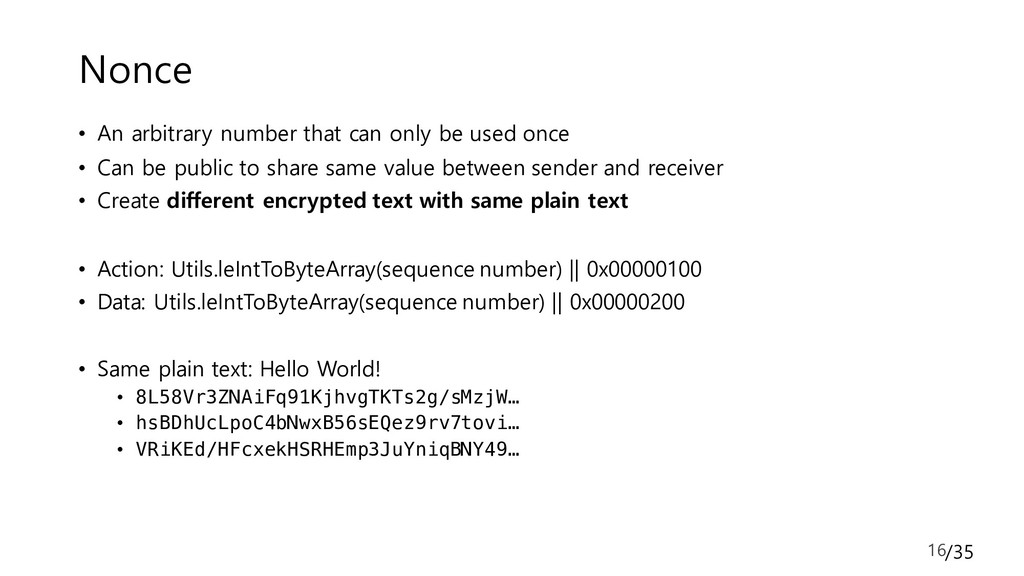
used once • Can be public to share same value between sender and receiver • Create different encrypted text with same plain text • Action: Utils.leIntToByteArray(sequence number) || 0x00000100 • Data: Utils.leIntToByteArray(sequence number) || 0x00000200 • Same plain text: Hello World! • 8L58Vr3ZNAiFq91KjhvgTKTs2g/sMzjW… • hsBDhUcLpoC4bNwxB56sEQez9rv7tovi… • VRiKEd/HFcxekHSRHEmp3JuYniqBNY49… 16
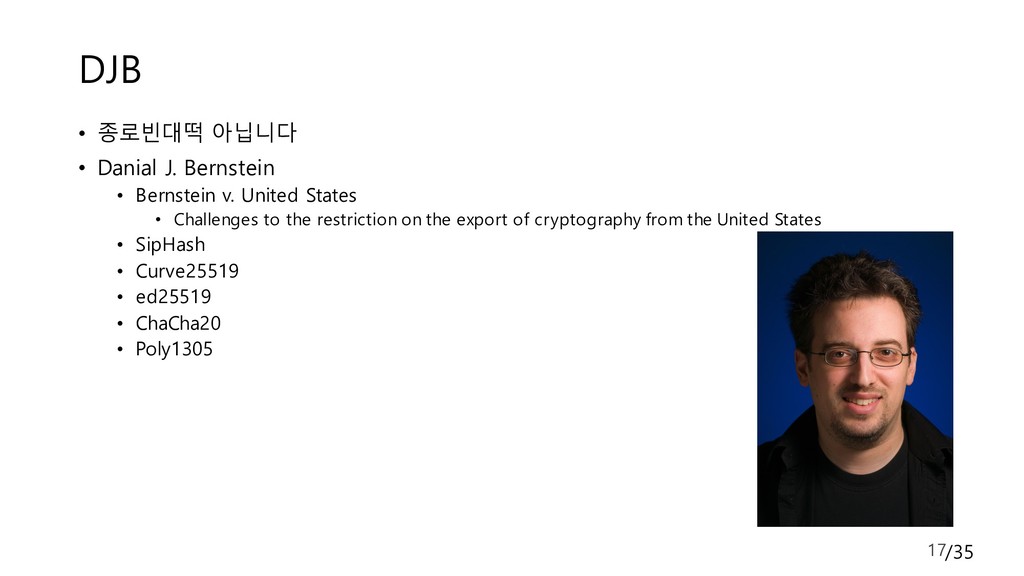
Bernstein v. United States • Challenges to the restriction on the export of cryptography from the United States • SipHash • Curve25519 • ed25519 • ChaCha20 • Poly1305 17
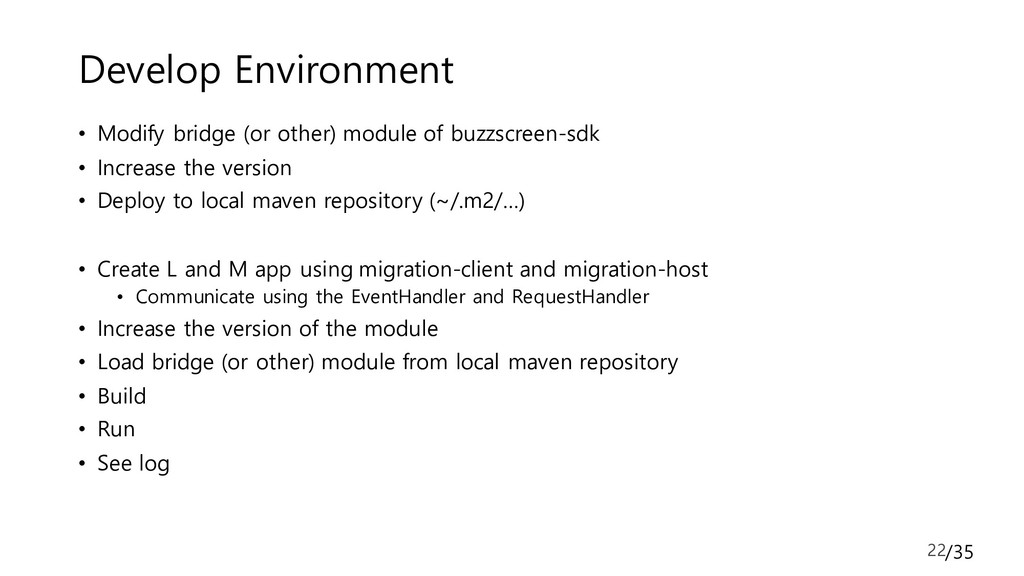
buzzscreen-sdk • Increase the version • Deploy to local maven repository (~/.m2/…) • Create L and M app using migration-client and migration-host • Communicate using the EventHandler and RequestHandler • Increase the version of the module • Load bridge (or other) module from local maven repository • Build • Run • See log 22
packageName) • com.buzzvil.buzzscreen.bridge.MsgSender.init(context, packageName) • Each initializer initiate it’s CryptoManager • The receivers are set in the constructor of each CryptoManager 25
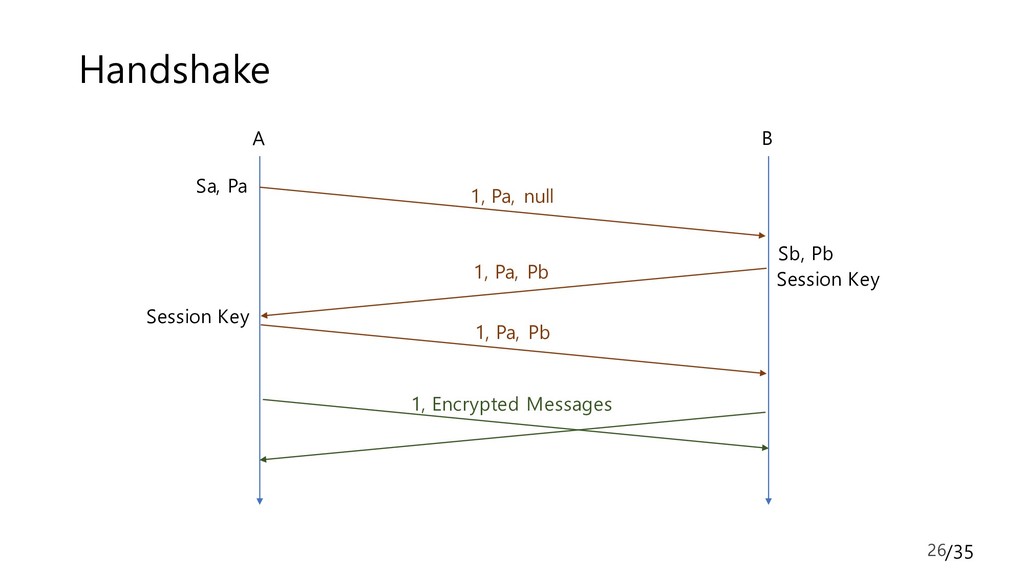
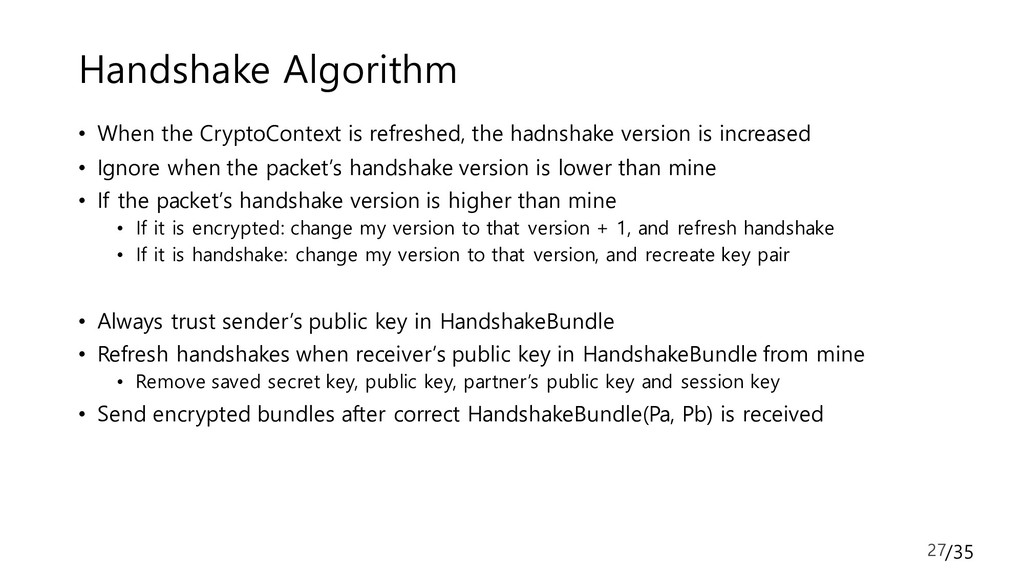
hadnshake version is increased • Ignore when the packet’s handshake version is lower than mine • If the packet’s handshake version is higher than mine • If it is encrypted: change my version to that version + 1, and refresh handshake • If it is handshake: change my version to that version, and recreate key pair • Always trust sender’s public key in HandshakeBundle • Refresh handshakes when receiver’s public key in HandshakeBundle from mine • Remove saved secret key, public key, partner’s public key and session key • Send encrypted bundles after correct HandshakeBundle(Pa, Pb) is received 27
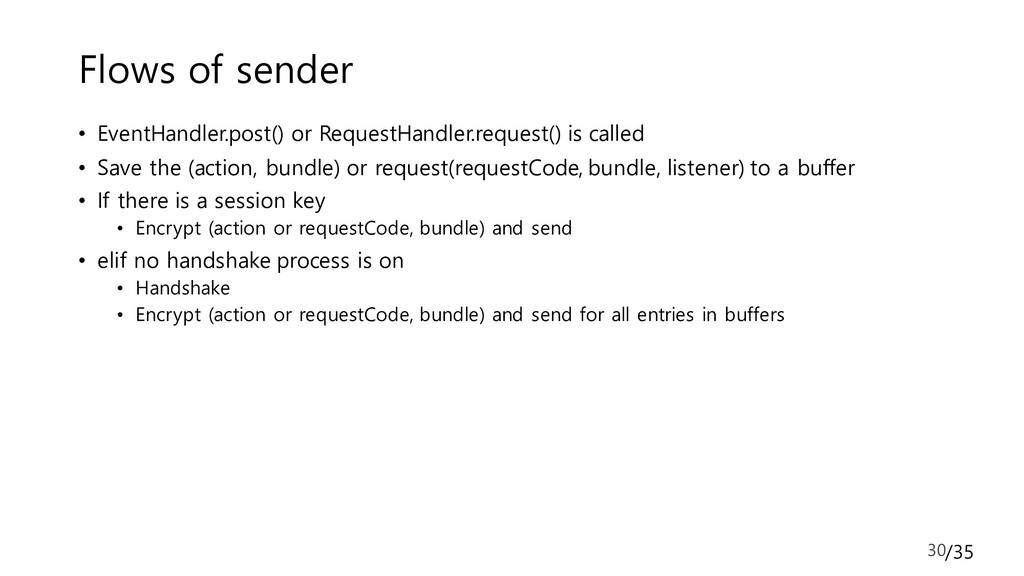
• Save the (action, bundle) or request(requestCode, bundle, listener) to a buffer • If there is a session key • Encrypt (action or requestCode, bundle) and send • elif no handshake process is on • Handshake • Encrypt (action or requestCode, bundle) and send for all entries in buffers 30
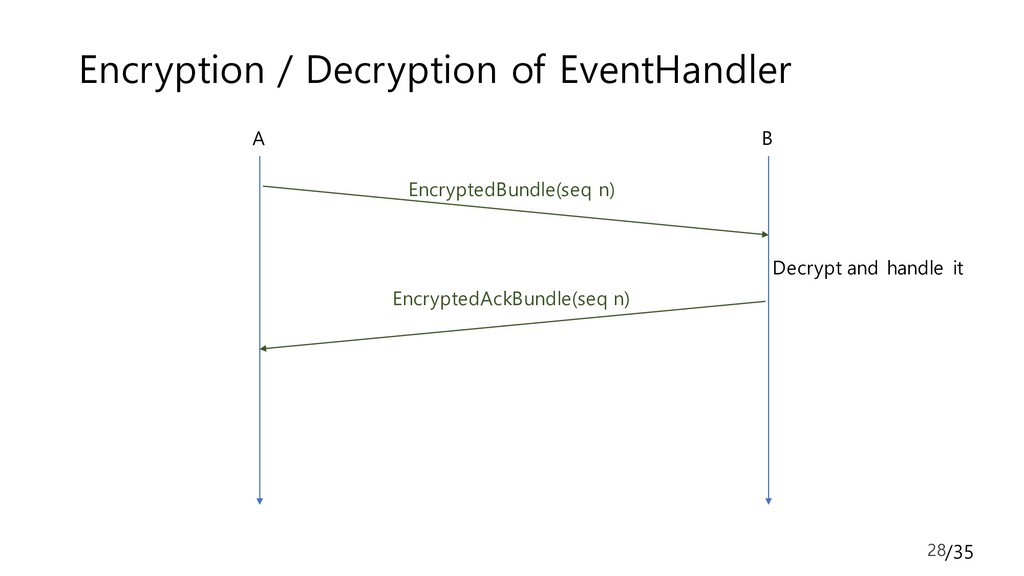
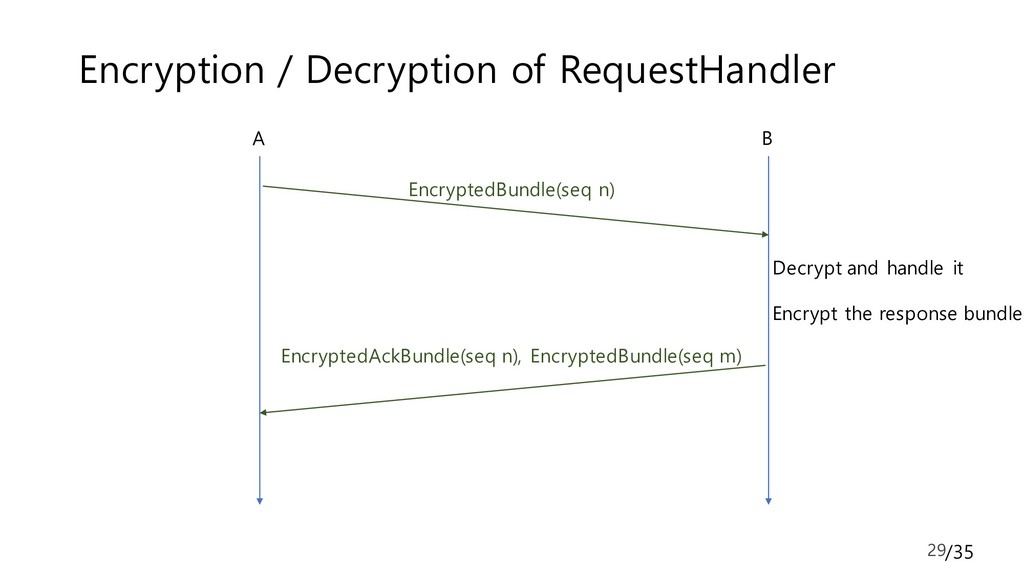
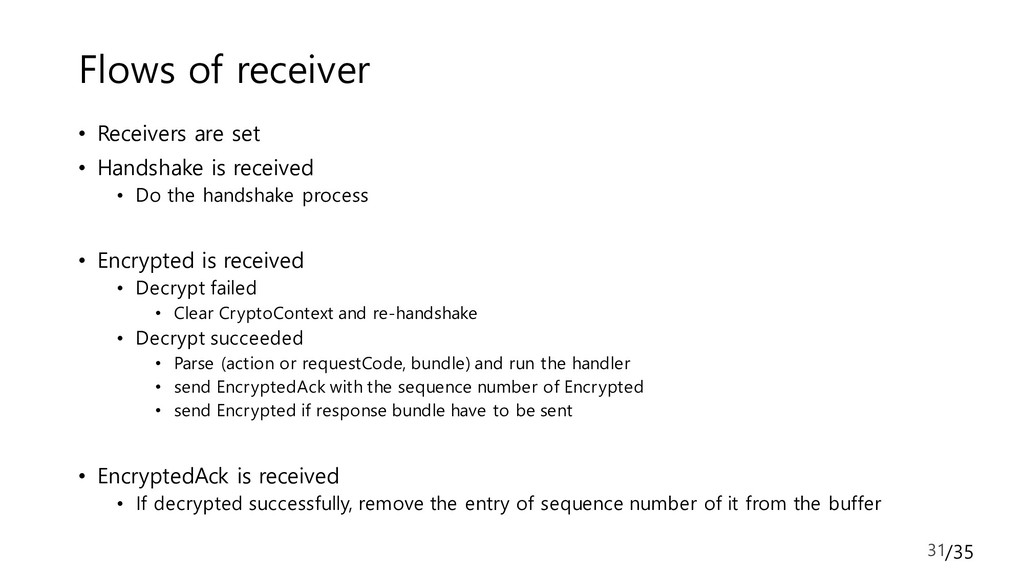
is received • Do the handshake process • Encrypted is received • Decrypt failed • Clear CryptoContext and re-handshake • Decrypt succeeded • Parse (action or requestCode, bundle) and run the handler • send EncryptedAck with the sequence number of Encrypted • send Encrypted if response bundle have to be sent • EncryptedAck is received • If decrypted successfully, remove the entry of sequence number of it from the buffer 31
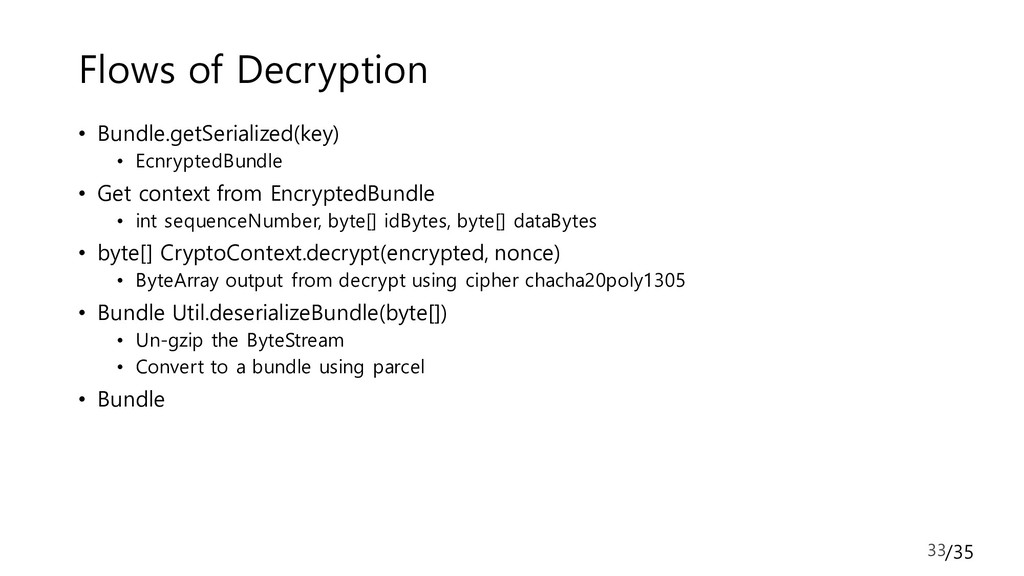
context from EncryptedBundle • int sequenceNumber, byte[] idBytes, byte[] dataBytes • byte[] CryptoContext.decrypt(encrypted, nonce) • ByteArray output from decrypt using cipher chacha20poly1305 • Bundle Util.deserializeBundle(byte[]) • Un-gzip the ByteStream • Convert to a bundle using parcel • Bundle 33
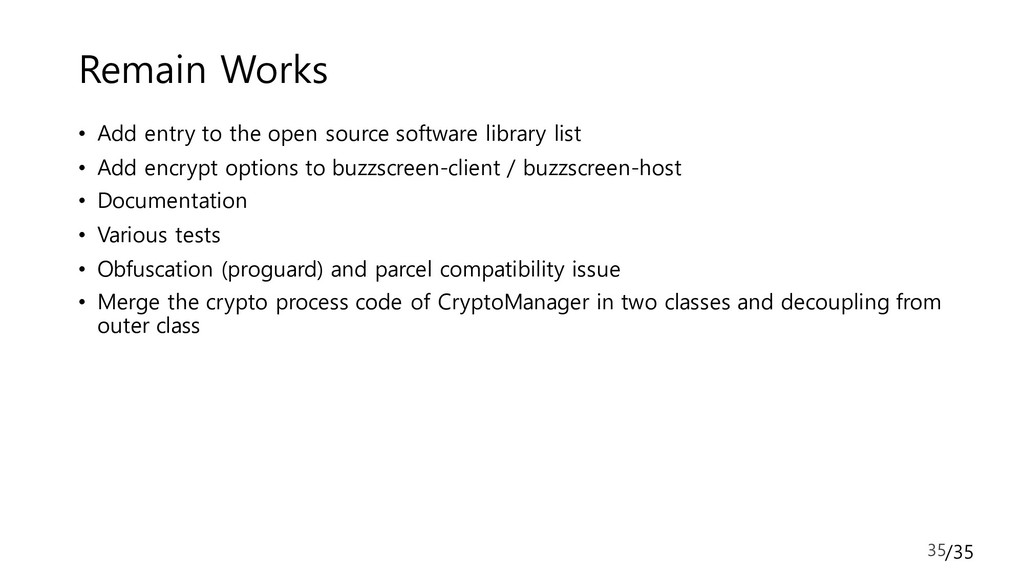
software library list • Add encrypt options to buzzscreen-client / buzzscreen-host • Documentation • Various tests • Obfuscation (proguard) and parcel compatibility issue • Merge the crypto process code of CryptoManager in two classes and decoupling from outer class 35


 buzzvil
 sms_tech
 ikura_hamu
 steliosf
 nakamizu
 yosuke_furukawa
 fuqda
 pvcresin
 chigichan24
 yuuu
 izawa
 dalinaum
 ivargrimstad
 skoyamalab
 lauravandoore
 samtorres
 reverentgeek
 stephaniewalter
 mfonobong
 baasie
 livdayseo
 watany
 jacobian
 twada
 aleyda