ONE THING • What events will destroy the business ? • What events will stop revenue ? • What events will slow revenue ? • revenue => production, sales, shipping or whatever your core business is. 4 Continuity
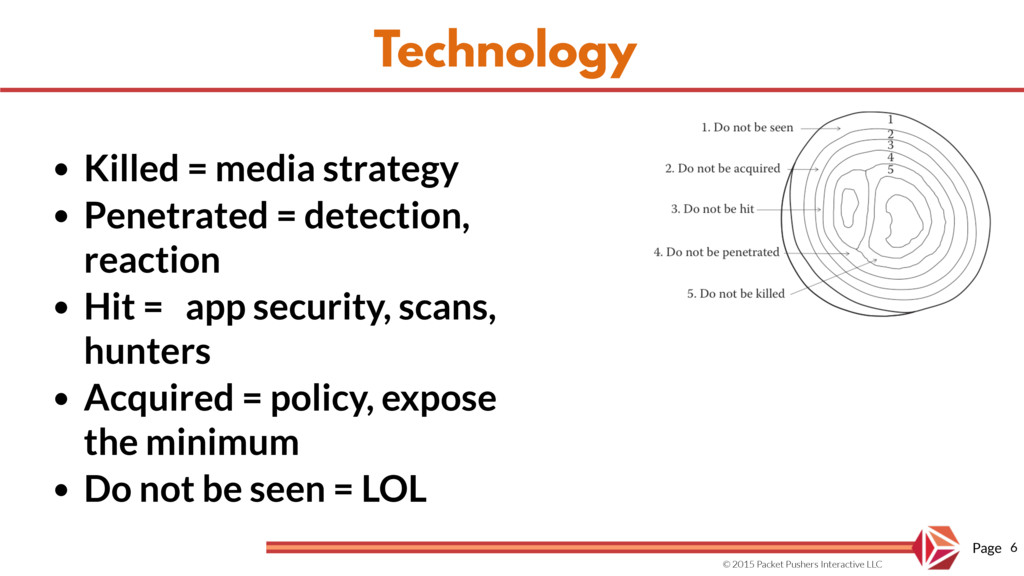
= media strategy • Penetrated = detection, reaction • Hit = app security, scans, hunters • Acquired = policy, expose the minimum • Do not be seen = LOL 6
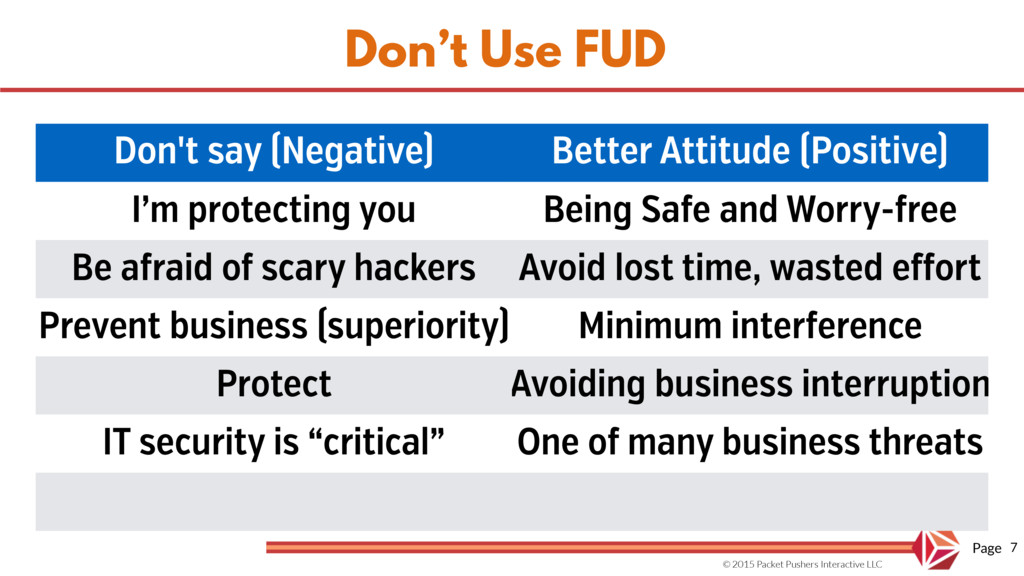
7 Don't say (Negative) Better Attitude (Positive) I’m protecting you Being Safe and Worry-free Be afraid of scary hackers Avoid lost time, wasted effort Prevent business (superiority) Minimum interference Protect Avoiding business interruption IT security is “critical” One of many business threats
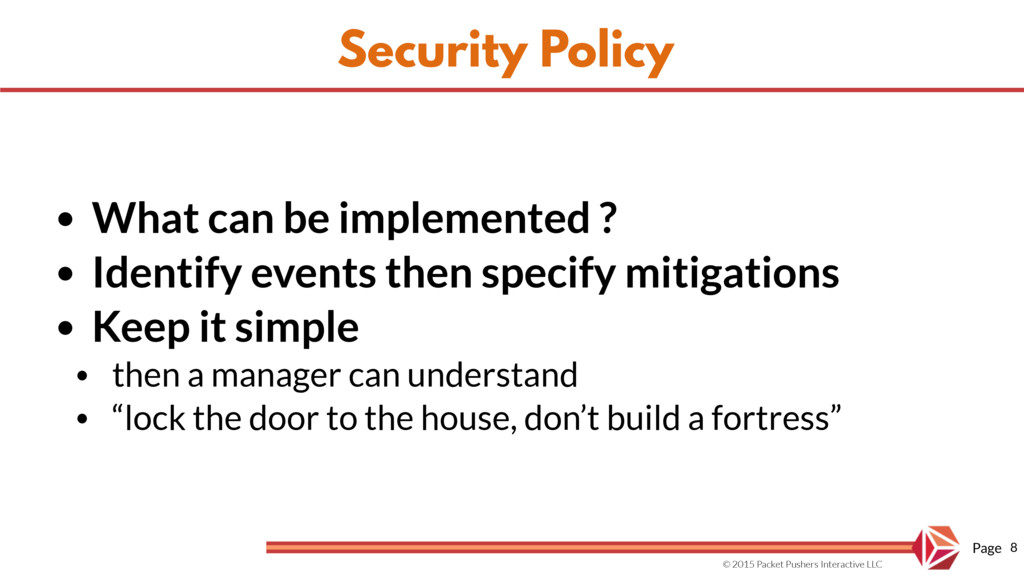
What can be implemented ? • Identify events then specify mitigations • Keep it simple • then a manager can understand • “lock the door to the house, don’t build a fortress” 8
Strategy • Assume you will be breached • SINGLE MOST IMPORTANT SECURITY STRATEGY • A great media plan will handle the breach as free marketing • Target, Homeland, • Ashley Madison • Heartland Payment Systems • did anyone go out of business ? Or did business get better…. 9
Most breaches are found by external parties • The first 12 hours of handling are critical • Plan • Who has to know ? Escalation path • What will they say ? (it doesn’t matter who) • have scripts ready to go • Verification • Have forensic tools 10
Physical Appliances are an operational nightmare • too many services on a single box creates huge problems • because of poor device control, every change can impact every other service • Reduce services per instance 13
Firewalls • Useful for control when servers aren’t protected • Bad for networking because they break paths and protocols • e.g.routing/redundancy • e.g. ICMP Echo, Path Asymmetry • Protocol Inspection is pointless • its all DNS, HTTP/S, SMTP these days. • more on this later 16
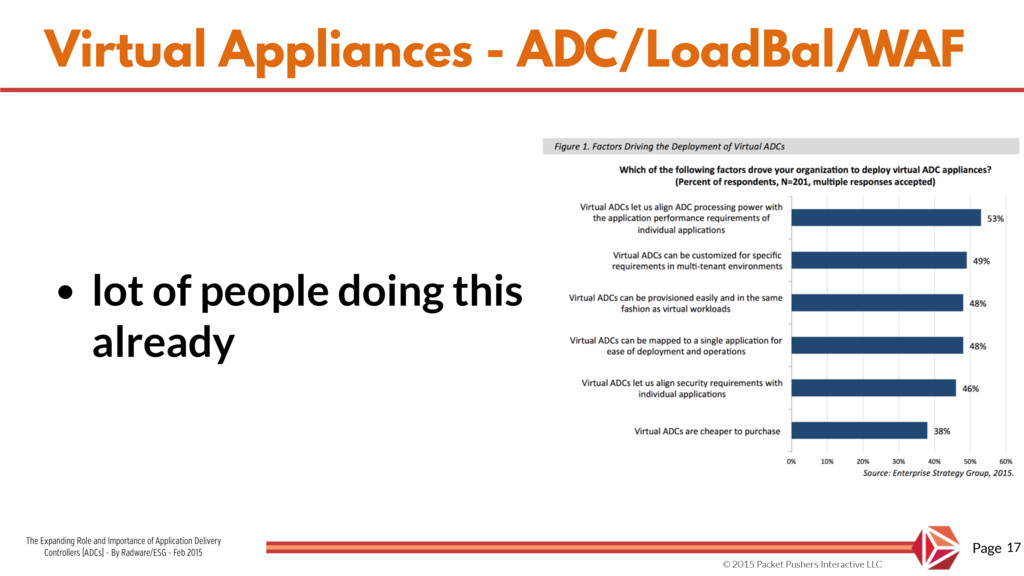
ADC/LoadBal/WAF • lot of people doing this already 17 The Expanding Role and Importance of Application Delivery Controllers (ADCs) - By Radware/ESG - Feb 2015
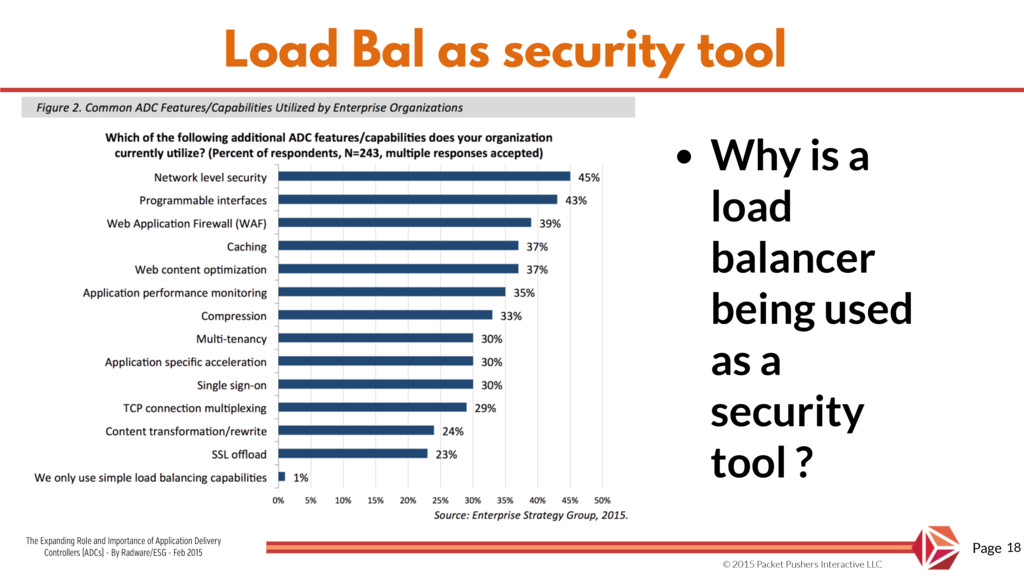
security tool • Why is a load balancer being used as a security tool ? 18 The Expanding Role and Importance of Application Delivery Controllers (ADCs) - By Radware/ESG - Feb 2015
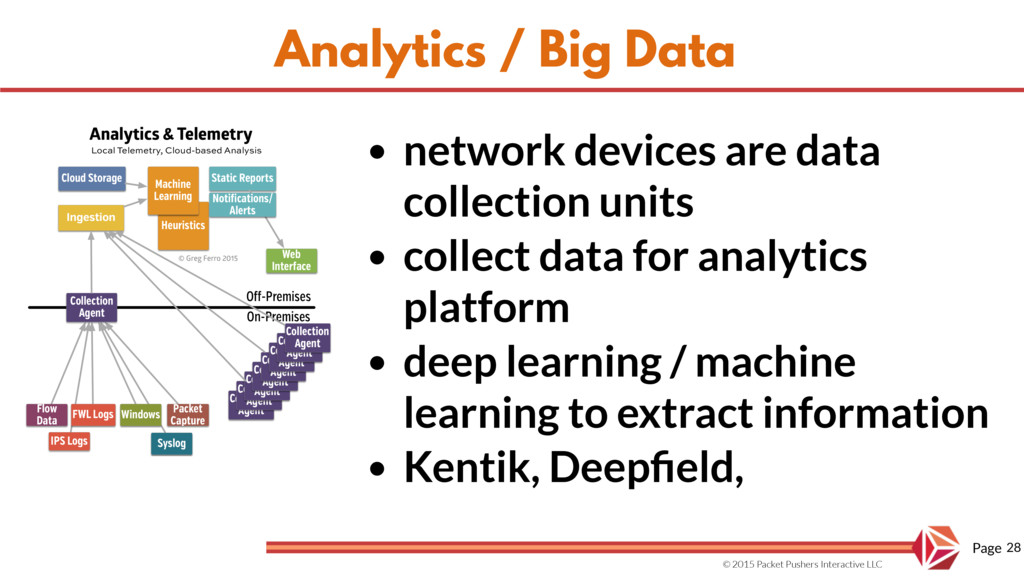
Security • Network Micro-Segmentation • Data-centric Application Inspection /Awareness • Lateral Detection and Prevention • Analytics / Big Data (measureable policy) 21 Lets look at each of these
2 • VLANs are network segmentation • MPLS is network segmentation • ACLs are network segmentation • Segmentation isn’t new, OK. • has been an operational disaster • VLANs & MPLS are network centric not application centric 23
3 • Need Segmentation that servers can use. • Goal: Application security not VLAN/VRF security • SDN created orchestration between OS/VM/ Container/Network, • Overlays are practical because of SDN • Not just one but MANY overlays 24
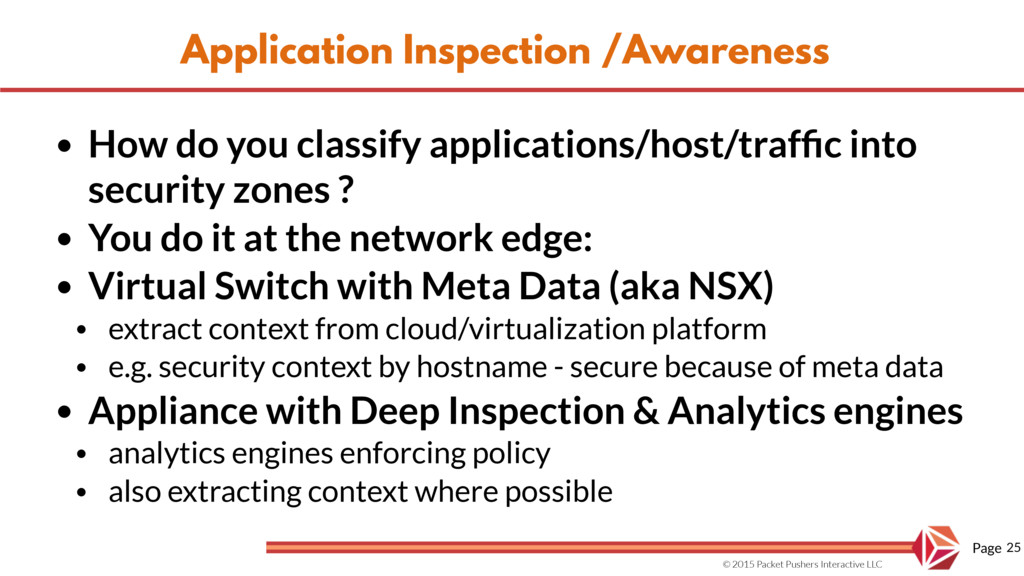
• How do you classify applications/host/traffic into security zones ? • You do it at the network edge: • Virtual Switch with Meta Data (aka NSX) • extract context from cloud/virtualization platform • e.g. security context by hostname - secure because of meta data • Appliance with Deep Inspection & Analytics engines • analytics engines enforcing policy • also extracting context where possible 25
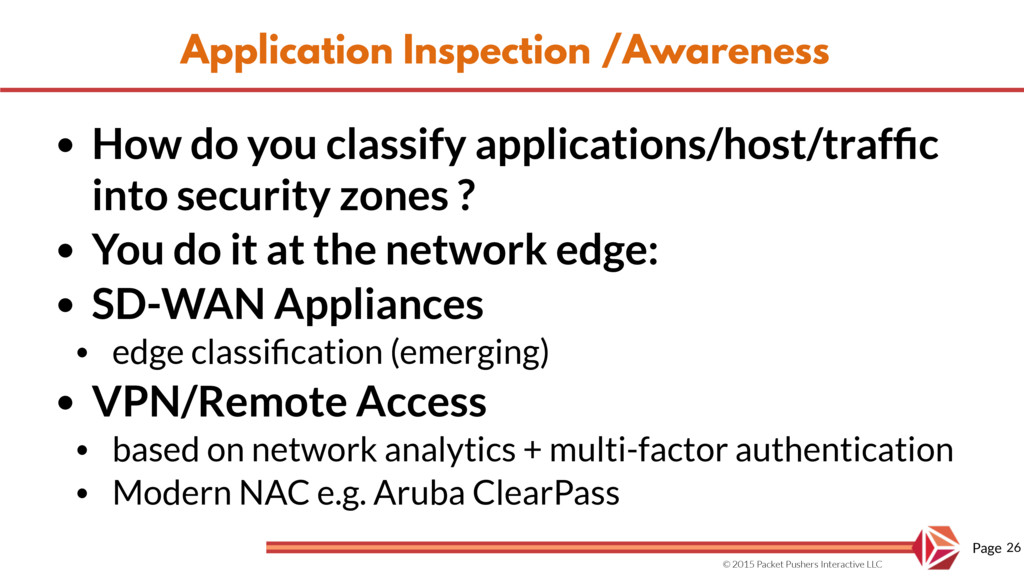
• How do you classify applications/host/traffic into security zones ? • You do it at the network edge: • SD-WAN Appliances • edge classification (emerging) • VPN/Remote Access • based on network analytics + multi-factor authentication • Modern NAC e.g. Aruba ClearPass 26
Once you have been breached, the media strategy requires that you can back up your claims • Have forensic tools for playback • Packet capture e.g. Endace. • Log 29


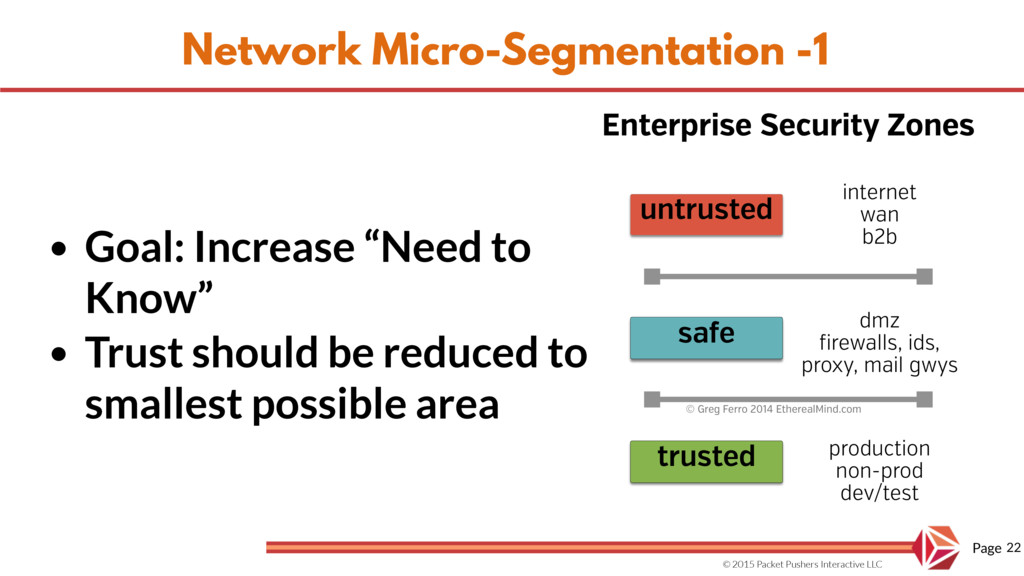
 etherealmind
 teru0x1
 fullkaiten
 k1nakayama
 kawaguti
 tomodakengo
 ysasago
 keitah
 techtekt
 nenonaninu
 m3m0r7
 philipz
 ren8k
 signer
 baasie
 konakalab
 lauravandoore
 sferik
 techseoconnect
 frankvandijk
 akademiya2063
 scottboms
 bluesmoon
 cargoodrich
 skipperchong