Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
20190705_CloudNativeKansai__4.pdf
Search
nezumisannn
July 05, 2019
Technology
530
3
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
20190705_CloudNativeKansai__4.pdf
nezumisannn
July 05, 2019
Transcript
42 slides
Packer/Ansible/Terraformを使った AWS Fargateへのデプロイ Cloud Native Kansai #4 株式会社ビヨンド 寺岡 佑樹
はじめに ・本資料は後日公開します ・資料中に記載されているコードGitHubに公開しています https://github.com/nezumisannn/aws-fargate-pipeline-example ・資料公開したらTwitterでハッシュタグ付きでつぶやきます
Agenda ・自己紹介 ・利用するツール/サービスの紹介 ・このスライドで作れる環境の構成図 ・環境の作り方 ・まとめ
自己紹介 resource “my_profile” “nezumisannn” { name = “Yuki.Teraoka” nickname =
“ねずみさん家。” company = “beyond” job = “Site Reliability Engineer” twitter = “@yktr_sre” skills = [“terraform”,”packer”] }
利用するツール
利用するツール Terraform Packer Ansible
利用するサービス
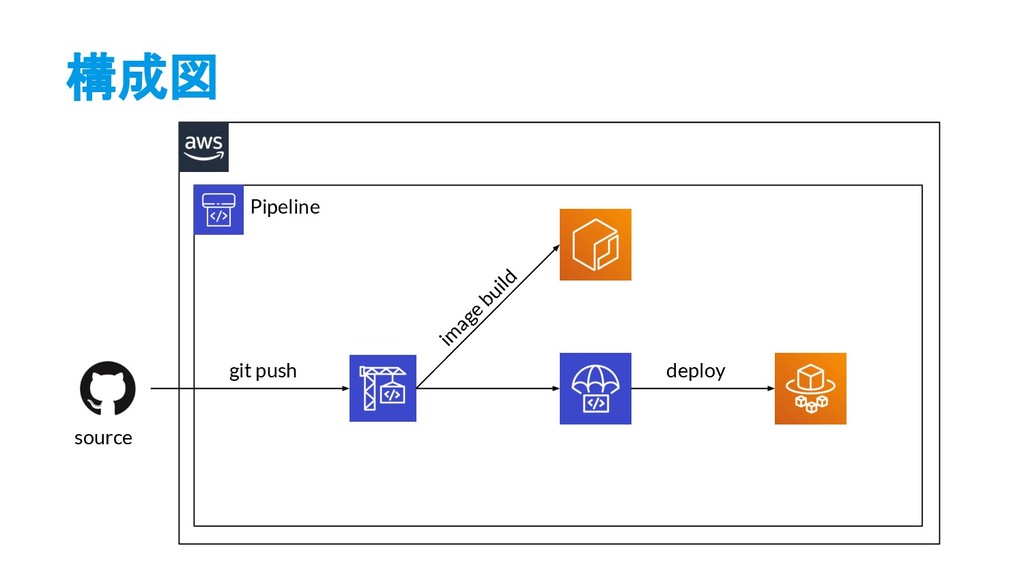
利用するサービス Elastic Container Registry Fargate Code Build Code Deploy Code
Pipeline
構成図
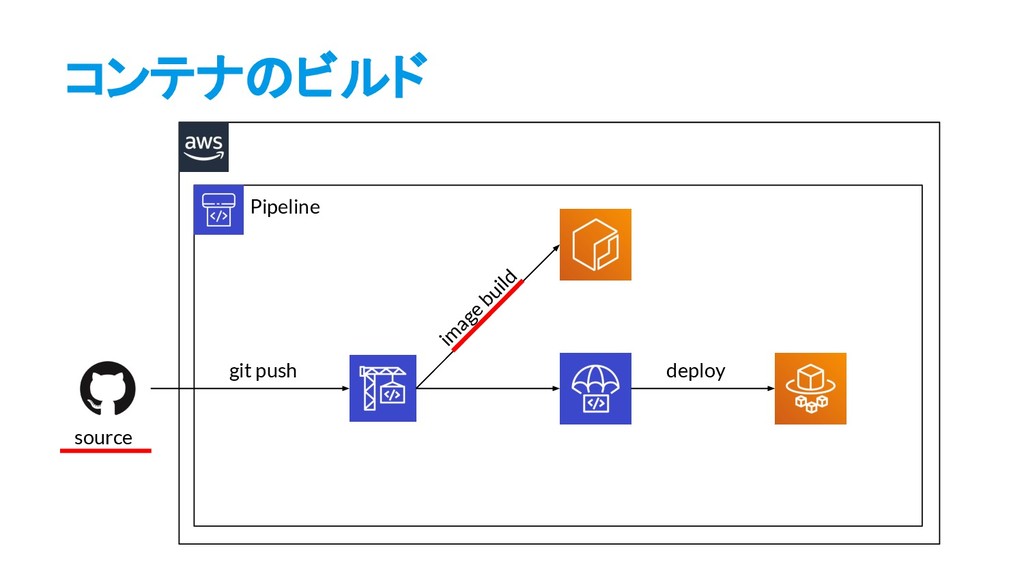
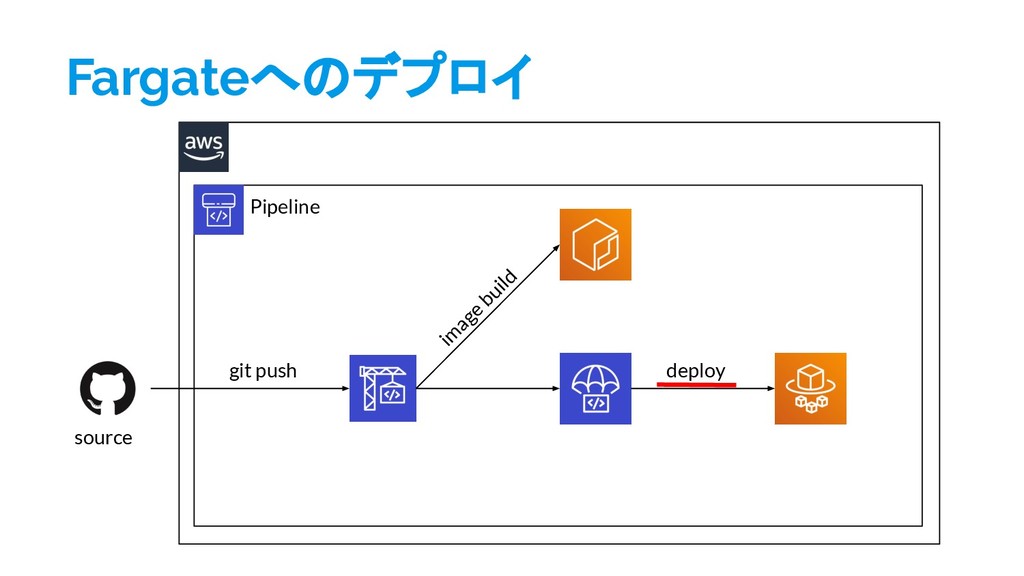
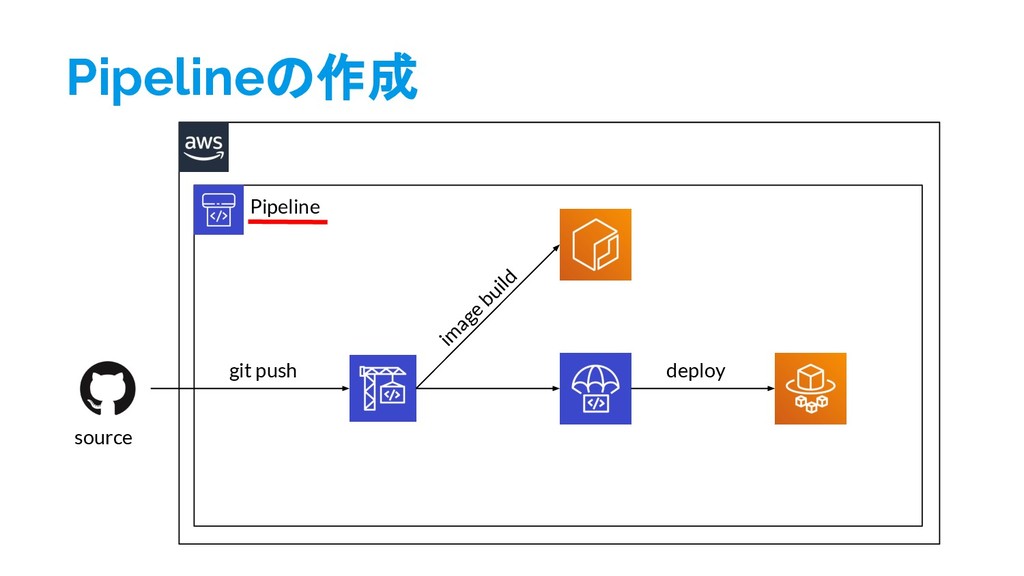
構成図 Pipeline git push im age build deploy source
出来ること ・fargateへのデプロイの自動化(CI/CD) ・GitへのPushをトリガーに、Pull ⇒ Build ⇒ Deployまで処理できる
デモ
今回のゴール ・CodePipelineの一連の処理を実行できる ・実行した結果、ブラウザの画面に「hello world」と表示されるようにする
実装
コンテナのビルド Pipeline git push im age build deploy source
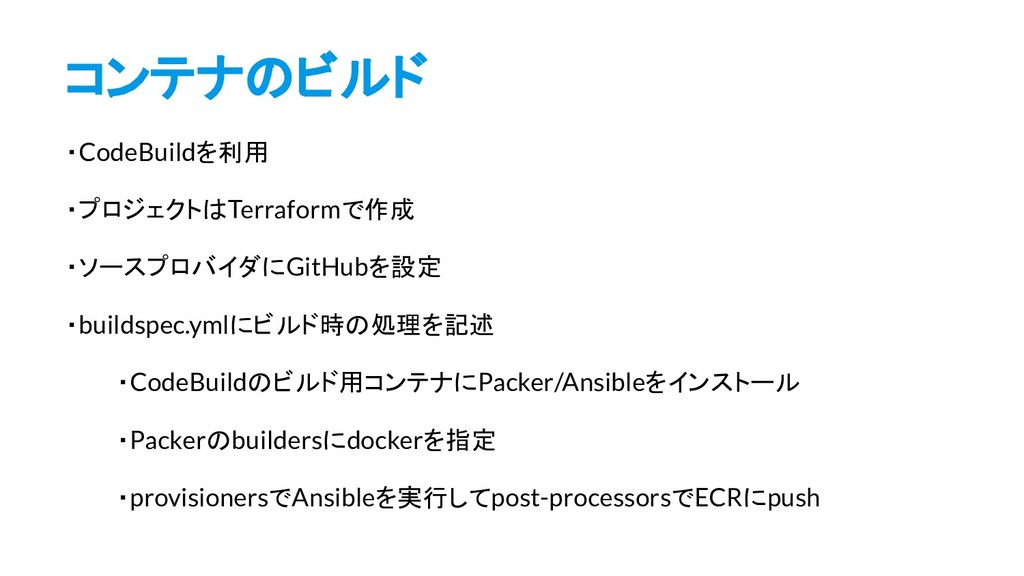
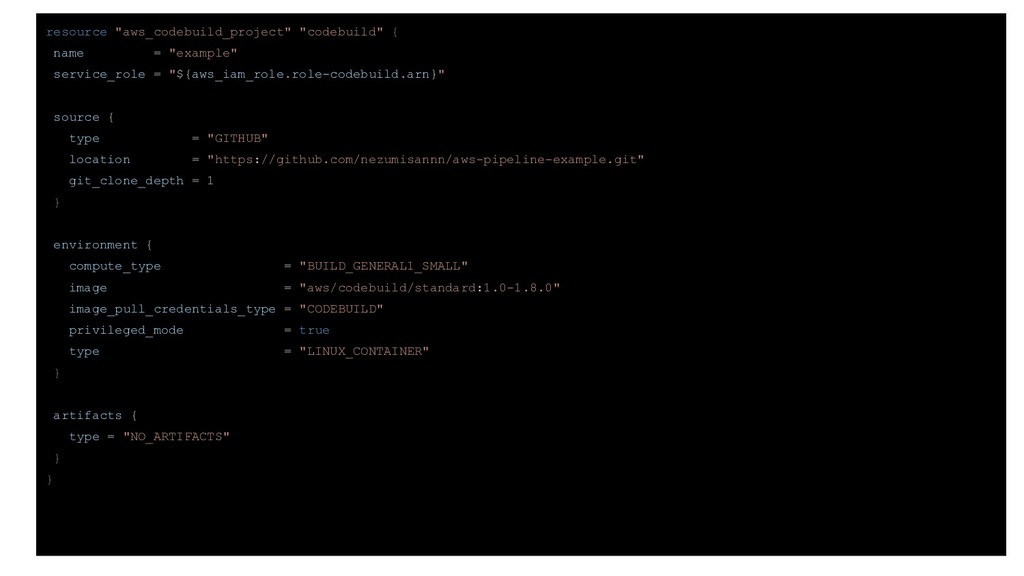
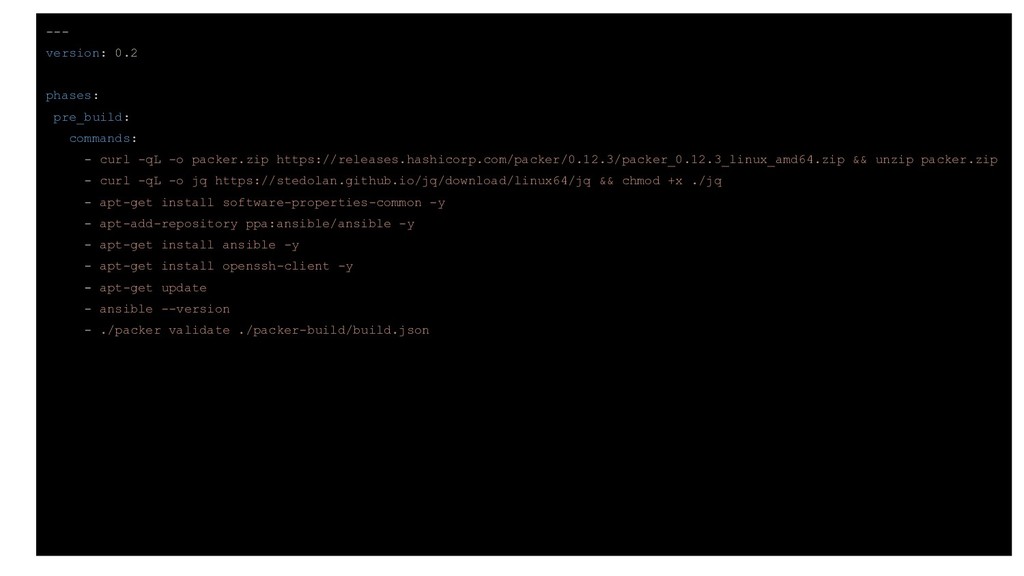
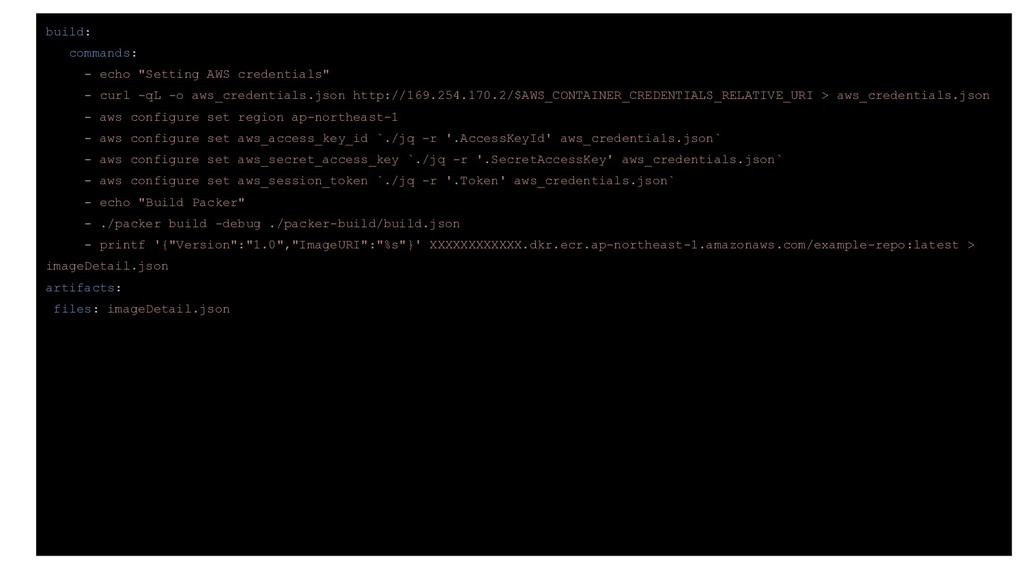
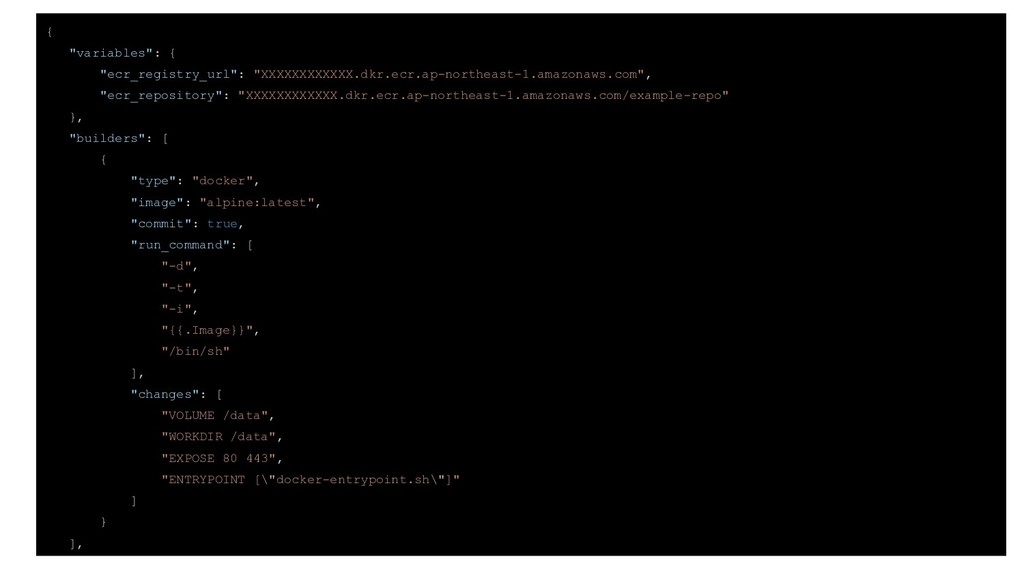
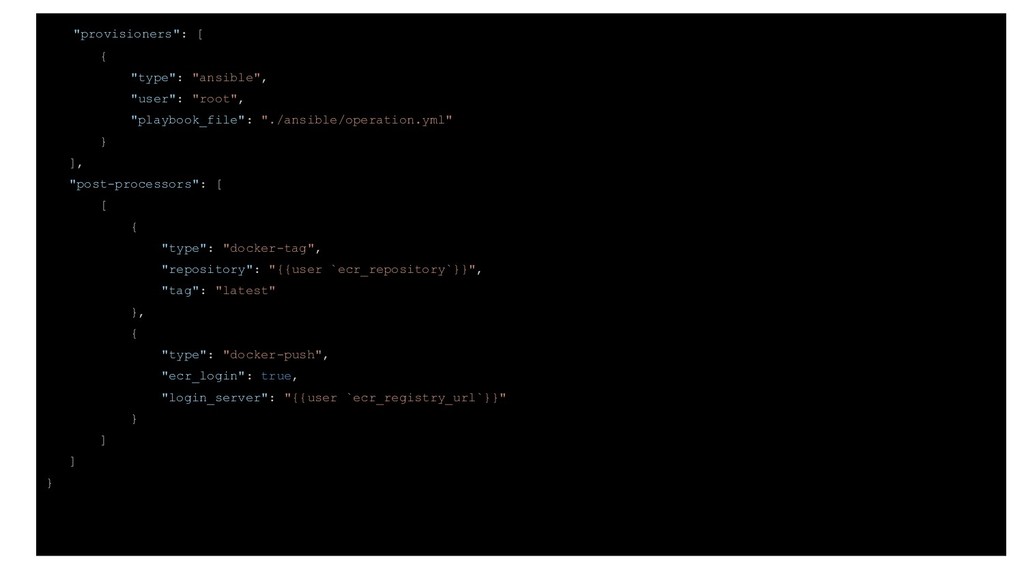
コンテナのビルド ・CodeBuildを利用 ・プロジェクトはTerraformで作成 ・ソースプロバイダにGitHubを設定 ・buildspec.ymlにビルド時の処理を記述 ・CodeBuildのビルド用コンテナにPacker/Ansibleをインストール ・Packerのbuildersにdockerを指定 ・provisionersでAnsibleを実行してpost-processorsでECRにpush
resource "aws_codebuild_project" "codebuild" { name = "example" service_role = "${aws_iam_role.role-codebuild.arn}"
source { type = "GITHUB" location = "https://github.com/nezumisannn/aws-pipeline-example.git" git_clone_depth = 1 } environment { compute_type = "BUILD_GENERAL1_SMALL" image = "aws/codebuild/standard:1.0-1.8.0" image_pull_credentials_type = "CODEBUILD" privileged_mode = true type = "LINUX_CONTAINER" } artifacts { type = "NO_ARTIFACTS" } }
--- version: 0.2 phases: pre_build: commands: - curl -qL -o
packer.zip https://releases.hashicorp.com/packer/0.12.3/packer_0.12.3_linux_amd64.zip && unzip packer.zip - curl -qL -o jq https://stedolan.github.io/jq/download/linux64/jq && chmod +x ./jq - apt-get install software-properties-common -y - apt-add-repository ppa:ansible/ansible -y - apt-get install ansible -y - apt-get install openssh-client -y - apt-get update - ansible --version - ./packer validate ./packer-build/build.json
build: commands: - echo "Setting AWS credentials" - curl -qL
-o aws_credentials.json http://169.254.170.2/$AWS_CONTAINER_CREDENTIALS_RELATIVE_URI > aws_credentials.json - aws configure set region ap-northeast-1 - aws configure set aws_access_key_id `./jq -r '.AccessKeyId' aws_credentials.json` - aws configure set aws_secret_access_key `./jq -r '.SecretAccessKey' aws_credentials.json` - aws configure set aws_session_token `./jq -r '.Token' aws_credentials.json` - echo "Build Packer" - ./packer build -debug ./packer-build/build.json - printf '{"Version":"1.0","ImageURI":"%s"}' XXXXXXXXXXXX.dkr.ecr.ap-northeast-1.amazonaws.com/example-repo:latest > imageDetail.json artifacts: files: imageDetail.json
{ "variables": { "ecr_registry_url": "XXXXXXXXXXXX.dkr.ecr.ap-northeast-1.amazonaws.com", "ecr_repository": "XXXXXXXXXXXX.dkr.ecr.ap-northeast-1.amazonaws.com/example-repo" }, "builders": [
{ "type": "docker", "image": "alpine:latest", "commit": true, "run_command": [ "-d", "-t", "-i", "{{.Image}}", "/bin/sh" ], "changes": [ "VOLUME /data", "WORKDIR /data", "EXPOSE 80 443", "ENTRYPOINT [\"docker-entrypoint.sh\"]" ] } ],
"provisioners": [ { "type": "ansible", "user": "root", "playbook_file": "./ansible/operation.yml" }
], "post-processors": [ [ { "type": "docker-tag", "repository": "{{user `ecr_repository`}}", "tag": "latest" }, { "type": "docker-push", "ecr_login": true, "login_server": "{{user `ecr_registry_url`}}" } ] ] }
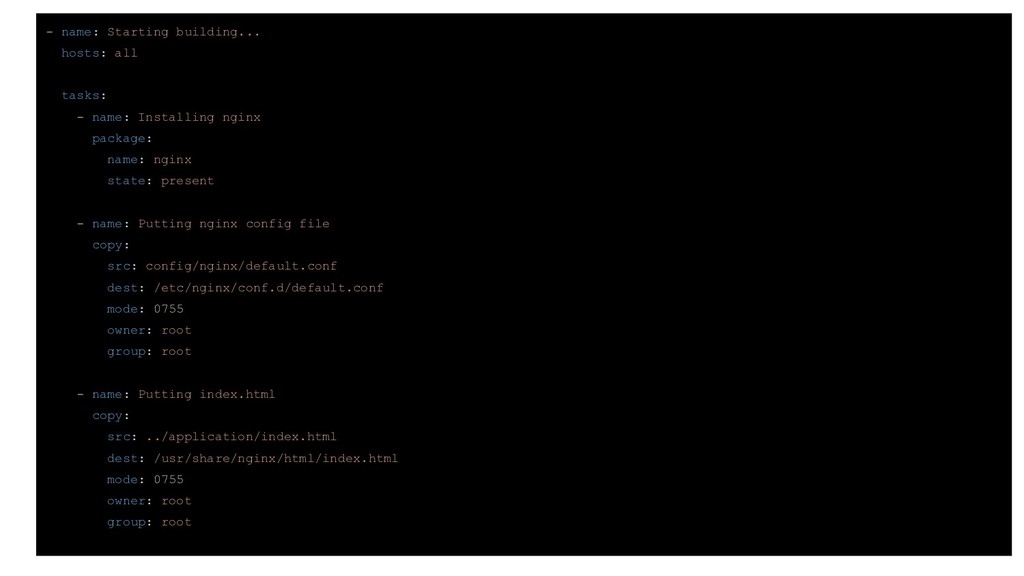
- name: Starting building... hosts: all tasks: - name: Installing
nginx package: name: nginx state: present - name: Putting nginx config file copy: src: config/nginx/default.conf dest: /etc/nginx/conf.d/default.conf mode: 0755 owner: root group: root - name: Putting index.html copy: src: ../application/index.html dest: /usr/share/nginx/html/index.html mode: 0755 owner: root group: root
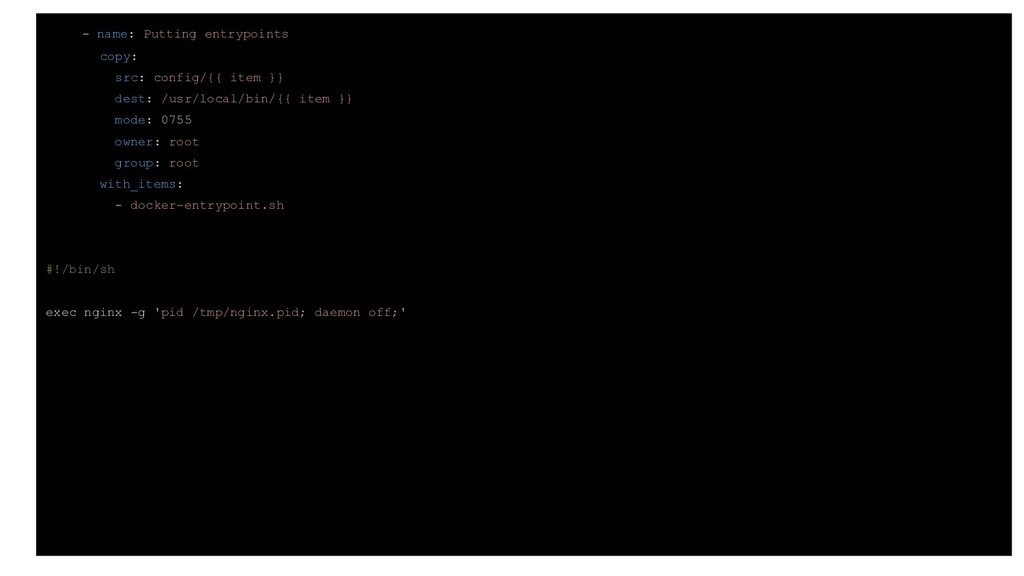
- name: Putting entrypoints copy: src: config/{{ item }} dest:
/usr/local/bin/{{ item }} mode: 0755 owner: root group: root with_items: - docker-entrypoint.sh #!/bin/sh exec nginx -g 'pid /tmp/nginx.pid; daemon off;'
Fargateへのデプロイ Pipeline git push im age build deploy source
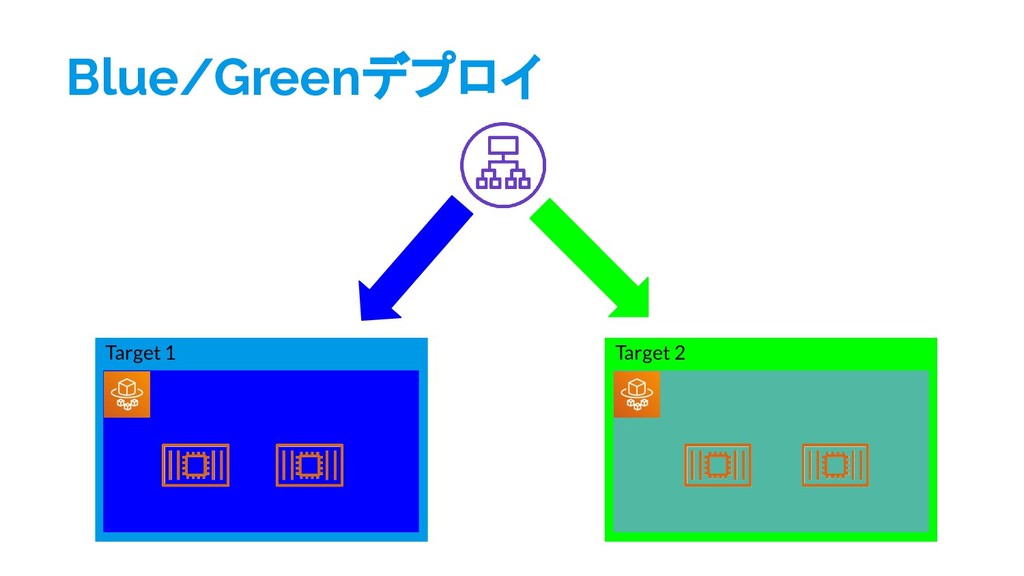
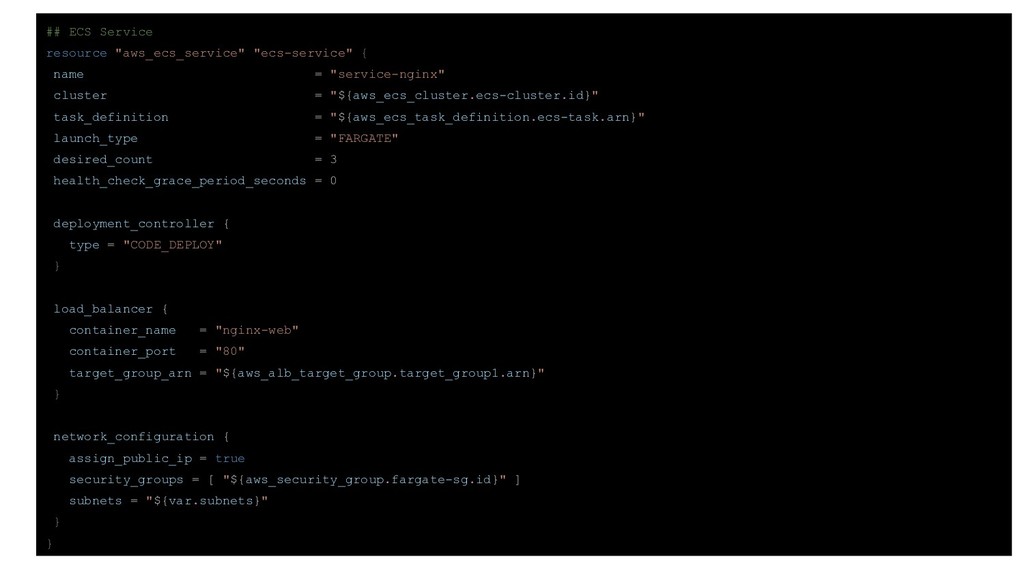
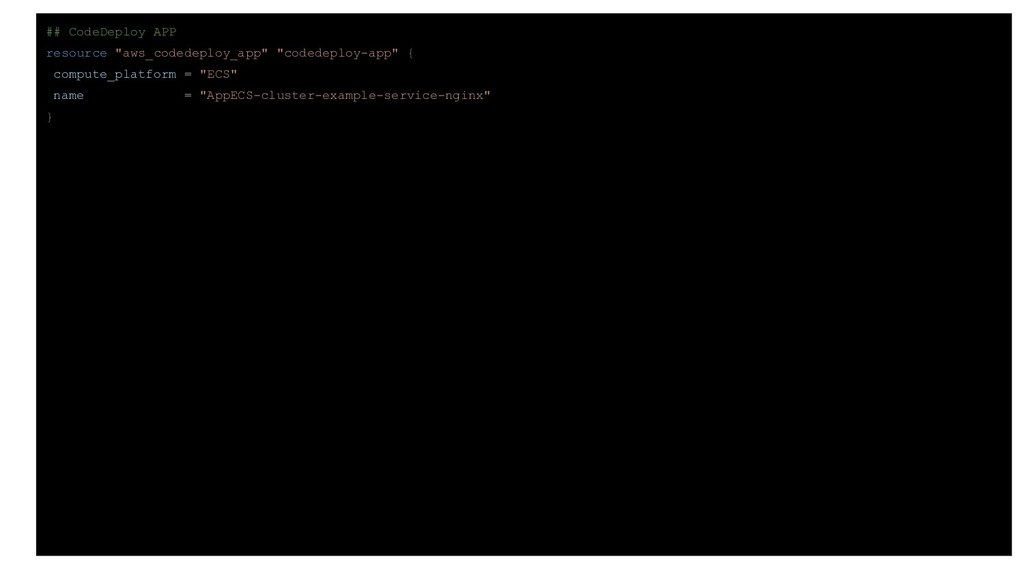
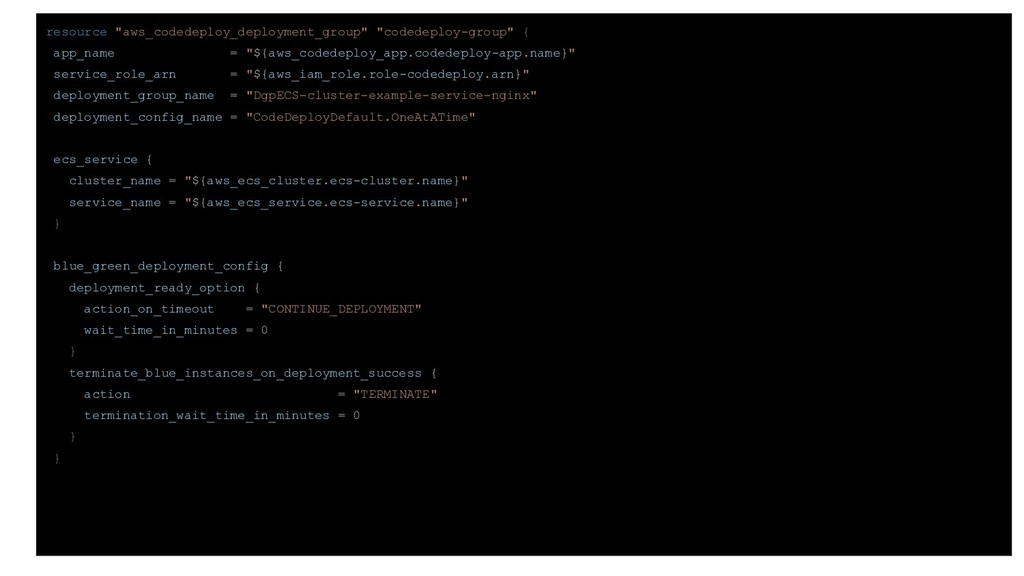
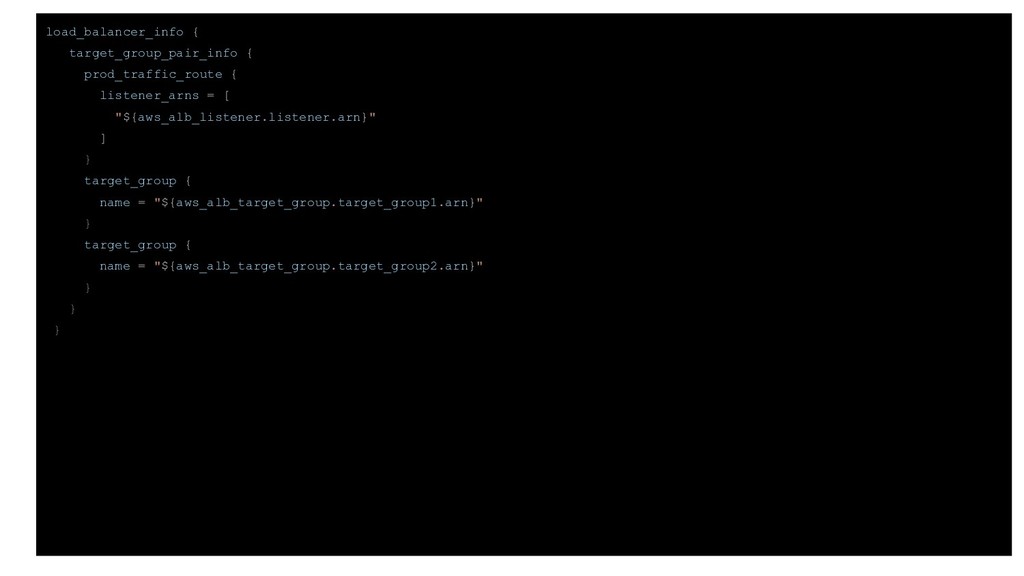
Fargateへのデプロイ ・CodeDeployを利用 ・Fargateとデプロイに必要なALB/ターゲットグループはTerraformで作成 ・ローリングアップデートではなくBlue/Greenデプロイを行う
Blue/Greenデプロイ Target 1 Target 2
resource "aws_alb" "alb" { name = "example" security_groups = ["${aws_security_group.alb-sg.id}"]
subnets = "${var.subnets}" }
## Target Group resource "aws_alb_target_group" "target_group1" { name = "example-tg1"
port = 80 protocol = "HTTP" target_type = "ip" vpc_id = "${var.vpc_id}" } resource "aws_alb_target_group" "target_group2" { name = "example-tg2" port = 80 protocol = "HTTP" target_type = "ip" vpc_id = "${var.vpc_id}" }
## ECS Service resource "aws_ecs_service" "ecs-service" { name = "service-nginx"
cluster = "${aws_ecs_cluster.ecs-cluster.id}" task_definition = "${aws_ecs_task_definition.ecs-task.arn}" launch_type = "FARGATE" desired_count = 3 health_check_grace_period_seconds = 0 deployment_controller { type = "CODE_DEPLOY" } load_balancer { container_name = "nginx-web" container_port = "80" target_group_arn = "${aws_alb_target_group.target_group1.arn}" } network_configuration { assign_public_ip = true security_groups = [ "${aws_security_group.fargate-sg.id}" ] subnets = "${var.subnets}" } }
## CodeDeploy APP resource "aws_codedeploy_app" "codedeploy-app" { compute_platform = "ECS"
name = "AppECS-cluster-example-service-nginx" }
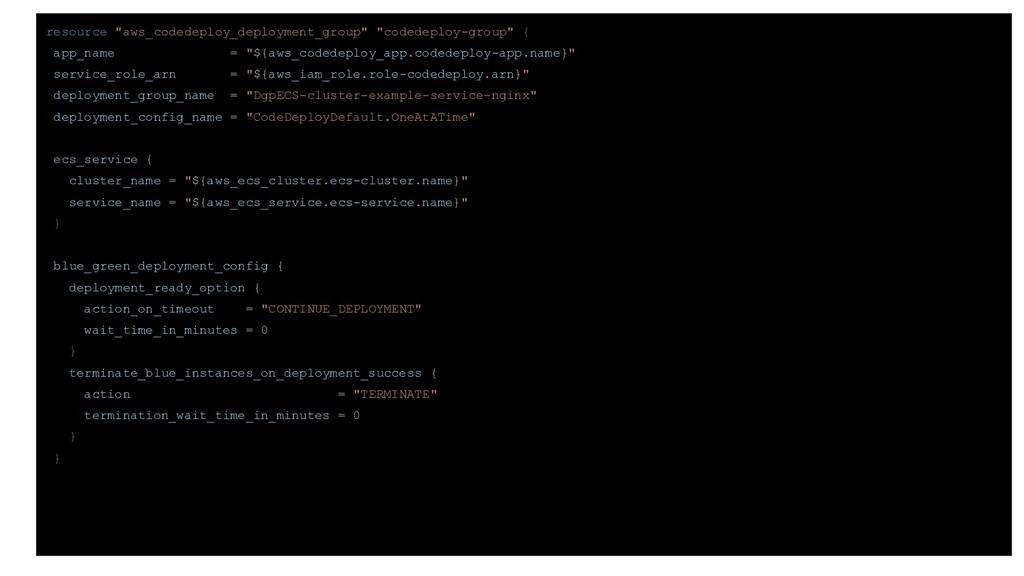
resource "aws_codedeploy_deployment_group" "codedeploy-group" { app_name = "${aws_codedeploy_app.codedeploy-app.name}" service_role_arn = "${aws_iam_role.role-codedeploy.arn}"
deployment_group_name = "DgpECS-cluster-example-service-nginx" deployment_config_name = "CodeDeployDefault.OneAtATime" ecs_service { cluster_name = "${aws_ecs_cluster.ecs-cluster.name}" service_name = "${aws_ecs_service.ecs-service.name}" } blue_green_deployment_config { deployment_ready_option { action_on_timeout = "CONTINUE_DEPLOYMENT" wait_time_in_minutes = 0 } terminate_blue_instances_on_deployment_success { action = "TERMINATE" termination_wait_time_in_minutes = 0 } }
load_balancer_info { target_group_pair_info { prod_traffic_route { listener_arns = [ "${aws_alb_listener.listener.arn}"
] } target_group { name = "${aws_alb_target_group.target_group1.arn}" } target_group { name = "${aws_alb_target_group.target_group2.arn}" } } }
resource "aws_codedeploy_deployment_group" "codedeploy-group" { app_name = "${aws_codedeploy_app.codedeploy-app.name}" service_role_arn = "${aws_iam_role.role-codedeploy.arn}"
deployment_group_name = "DgpECS-cluster-example-service-nginx" deployment_config_name = "CodeDeployDefault.OneAtATime" ecs_service { cluster_name = "${aws_ecs_cluster.ecs-cluster.name}" service_name = "${aws_ecs_service.ecs-service.name}" } blue_green_deployment_config { deployment_ready_option { action_on_timeout = "CONTINUE_DEPLOYMENT" wait_time_in_minutes = 0 } terminate_blue_instances_on_deployment_success { action = "TERMINATE" termination_wait_time_in_minutes = 0 } }
Pipelineの作成 Pipeline git push im age build deploy source
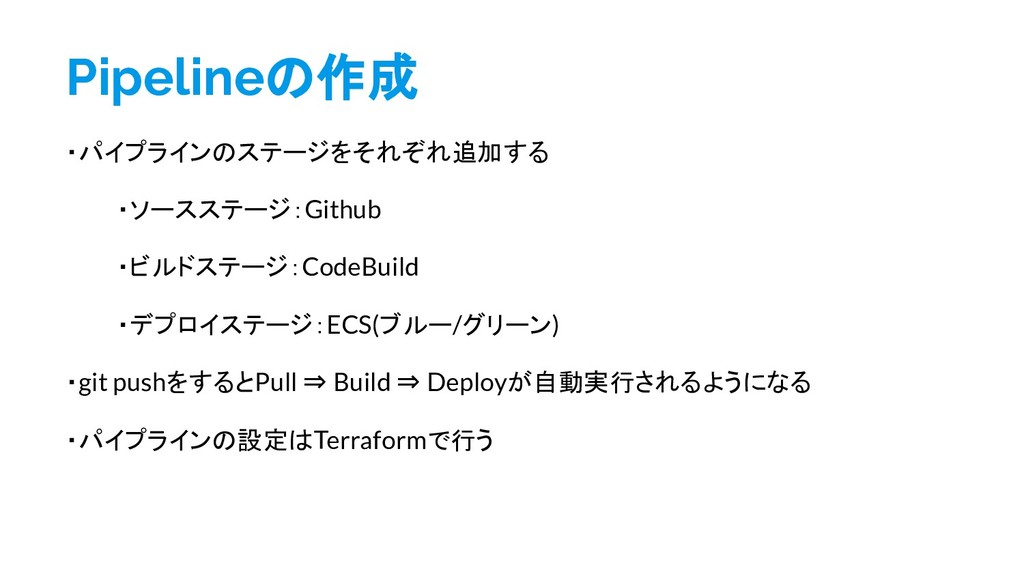
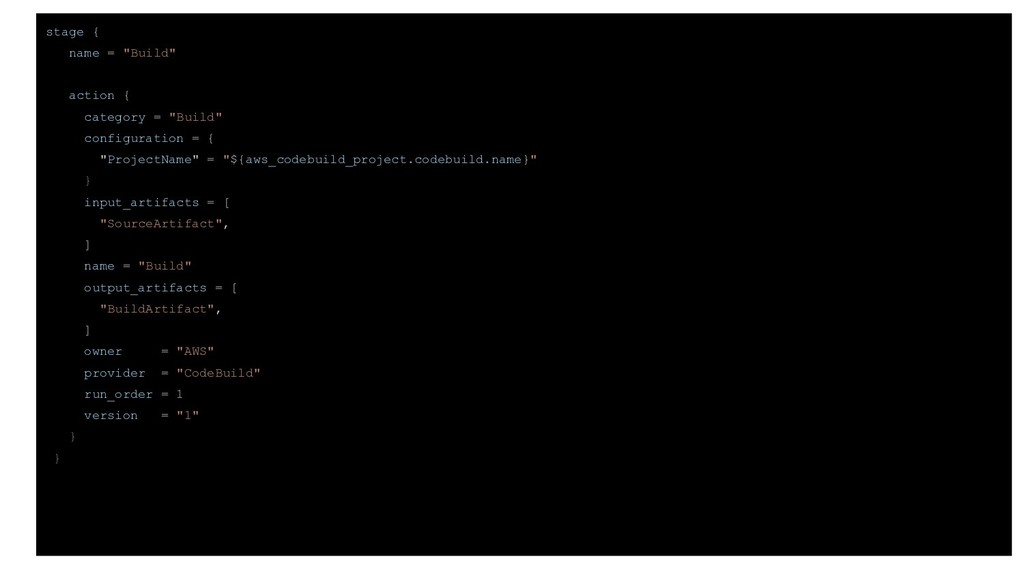
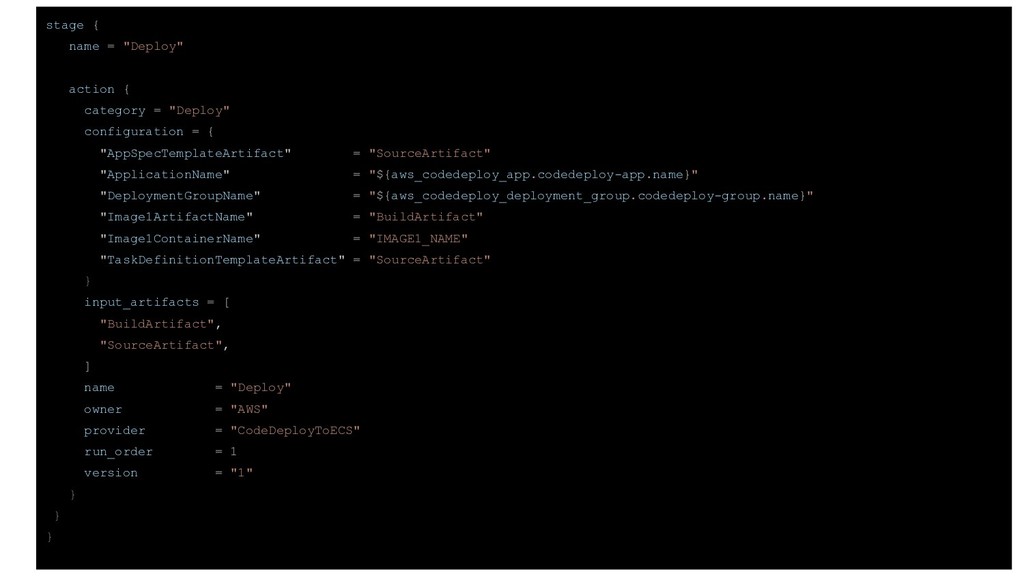
Pipelineの作成 ・パイプラインのステージをそれぞれ追加する ・ソースステージ:Github ・ビルドステージ:CodeBuild ・デプロイステージ:ECS(ブルー/グリーン) ・git pushをするとPull ⇒ Build ⇒
Deployが自動実行されるようになる ・パイプラインの設定はTerraformで行う
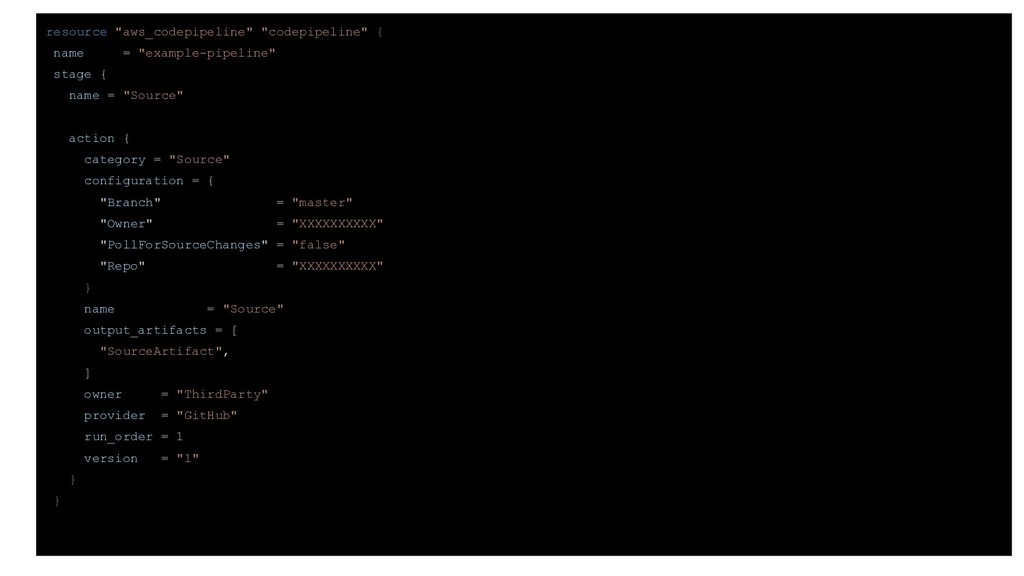
resource "aws_codepipeline" "codepipeline" { name = "example-pipeline" stage { name
= "Source" action { category = "Source" configuration = { "Branch" = "master" "Owner" = "XXXXXXXXXX" "PollForSourceChanges" = "false" "Repo" = "XXXXXXXXXX" } name = "Source" output_artifacts = [ "SourceArtifact", ] owner = "ThirdParty" provider = "GitHub" run_order = 1 version = "1" } }
stage { name = "Build" action { category = "Build"
configuration = { "ProjectName" = "${aws_codebuild_project.codebuild.name}" } input_artifacts = [ "SourceArtifact", ] name = "Build" output_artifacts = [ "BuildArtifact", ] owner = "AWS" provider = "CodeBuild" run_order = 1 version = "1" } }
stage { name = "Deploy" action { category = "Deploy"
configuration = { "AppSpecTemplateArtifact" = "SourceArtifact" "ApplicationName" = "${aws_codedeploy_app.codedeploy-app.name}" "DeploymentGroupName" = "${aws_codedeploy_deployment_group.codedeploy-group.name}" "Image1ArtifactName" = "BuildArtifact" "Image1ContainerName" = "IMAGE1_NAME" "TaskDefinitionTemplateArtifact" = "SourceArtifact" } input_artifacts = [ "BuildArtifact", "SourceArtifact", ] name = "Deploy" owner = "AWS" provider = "CodeDeployToECS" run_order = 1 version = "1" } } }
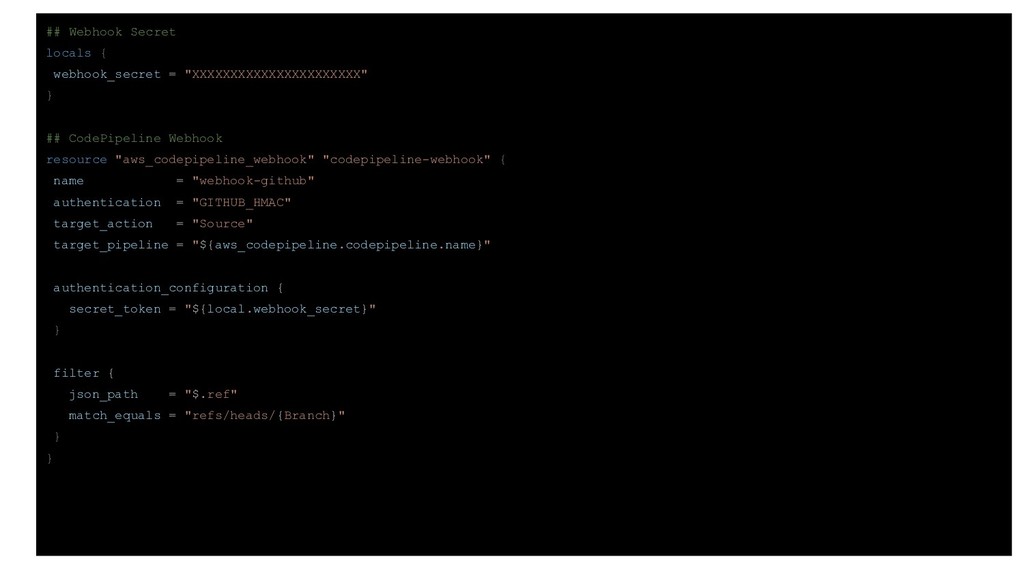
## Webhook Secret locals { webhook_secret = "XXXXXXXXXXXXXXXXXXXXXX" } ##
CodePipeline Webhook resource "aws_codepipeline_webhook" "codepipeline-webhook" { name = "webhook-github" authentication = "GITHUB_HMAC" target_action = "Source" target_pipeline = "${aws_codepipeline.codepipeline.name}" authentication_configuration { secret_token = "${local.webhook_secret}" } filter { json_path = "$.ref" match_equals = "refs/heads/{Branch}" } }
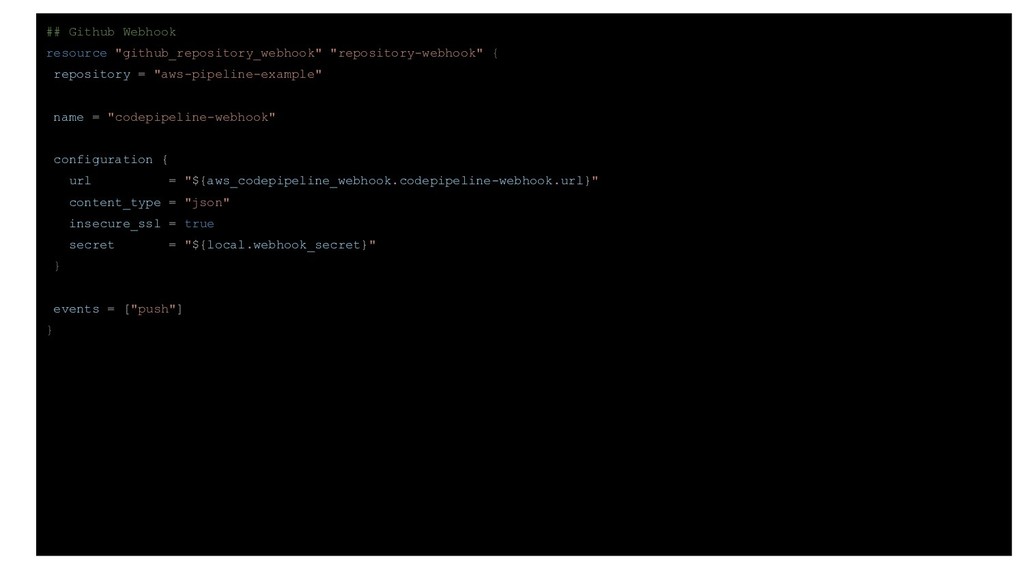
## Github Webhook resource "github_repository_webhook" "repository-webhook" { repository = "aws-pipeline-example"
name = "codepipeline-webhook" configuration { url = "${aws_codepipeline_webhook.codepipeline-webhook.url}" content_type = "json" insecure_ssl = true secret = "${local.webhook_secret}" } events = ["push"] }
まとめ ・FargateへのデプロイはAWSのデプロイ3兄弟を利用しよう ・OSSと組み合わせるとさらに便利に! ・デプロイ基盤を整えておくとリリース作業を省力化できる ・皆様のデプロイ基盤構築に役立てれば幸いです
END
More Decks by nezumisannn
See All by nezumisannn
20250930_Conohaウェビナー_生成AI_Terraform_ConoHa_VPSサーバー_セットアップ入門編
nezumisannn
1
48
20250723_Conohaウェビナー_高騰する海外クラウド費用を劇的カット_サーバーコスト最適化のポイント解説と成功事例のご紹介.pdf
nezumisannn
0
73
20241204_ビヨンド勉強会_44_AWS_Service_Catalogを利用したIaCのテンプレート化とTerraformによるデプロイ.pdf
nezumisannn
0
430
20240828_ビヨンド勉強会_42_EKS_on_FargateでWebサービスを公開するために覚えておきたいこと.pdf
nezumisannn
0
120
20240530_ビヨンド勉強会#41_ビヨンドのエンジニア新卒研修における取り組み
nezumisannn
0
140
20230511_AWSにおけるコンテナサービスの選択とIaC実装例.pdf
nezumisannn
0
1.5k
リーダーになって1年経過して_取り組んできたことと大事にしている考え方_の裏側_.pdf
nezumisannn
0
98
20211118_GKEにおける高負荷時のPodとWorker_Nodeの挙動について.pdf
nezumisannn
0
200
20211014_Alibaba_Cloud_Container_Service_for_KubernetesにおけるServerless_Kubernetesの概要とManaged_Kubernetesとの違い.pdf
nezumisannn
0
120
Other Decks in Technology
See All in Technology
Linuxネットワークスタック進化の軌跡: 過去10年の歩みと最新トレンド
orimanabu
4
710
Claude Securityを使ってみた / claude-security-claude-code-meetup-nagoya
tnir
0
120
Kiro IDE 入門 (画面の各部から、頼み方、任せ方、戻し方まで) | 目指せ Kiro マスター 02
inariku
PRO
4
250
BALLAS Technology Deck
ballas_inc
0
640
生成AI時代のIAMのマニアックな話
takuros
6
3.3k
速くなるほど、深く考える AI時代のQAに学ぶ
kobayashiyorimitsu
0
220
マネージャーをエスパーにしない マネジメントされる側から始める、働きやすい現場づくり
comi190327
0
510
An Introduction to Context Ontology Accelerator (teaching AI agents what your data means)
inariku
PRO
1
270
「任されビリティ」で引き受けて「よしなりてぃ」に頼らず任せる / Accept tasks with "makasarebility" and hand them over without relying on "yoshinarily"
pauli
0
630
Oracle Base Database Service 技術詳細
oracle4engineer
PRO
17
120k
MCPでネットワーク障害調査を自動化する前に直すべき3つのこと
yama3133
0
360
_マネジメントする人される人ナイト_2026__良いチームを作っていきたい_お気持ち_.pdf
xkxaxkx
0
530
Featured
See All Featured
So, you think you're a good person
axbom
PRO
2
2.3k
16th Malabo Montpellier Forum Presentation
akademiya2063
PRO
0
460
The browser strikes back
jonoalderson
0
1.9k
Tell your own story through comics
letsgokoyo
1
1.1k
GitHub's CSS Performance
jonrohan
1033
470k
Everyday Curiosity
cassininazir
0
400
Designing Experiences People Love
moore
143
24k
世界の人気アプリ100個を分析して見えたペイウォール設計の心得
akihiro_kokubo
PRO
74
43k
Scaling GitHub
holman
464
140k
Why Your Marketing Sucks and What You Can Do About It - Sophie Logan
marketingsoph
0
470
The Art of Delivering Value - GDevCon NA Keynote
reverentgeek
16
2.2k
How To Stay Up To Date on Web Technology
chriscoyier
790
250k


 nezumisannn
 orimanabu
 tnir
 inariku
 ballas_inc
 takuros
 kobayashiyorimitsu
 comi190327
 pauli
 oracle4engineer
 yama3133
 xkxaxkx
 axbom
 akademiya2063
 jonoalderson
 letsgokoyo
 jonrohan
 cassininazir
 moore
 akihiro_kokubo
 holman
 marketingsoph
 reverentgeek
 chriscoyier