Foundation Board Member @ CHAOSS Board Member @ Apereo Foundation [email protected] | @dizquierdo Ana Jiménez Santamaría Project Manager, Linux Foundation MSc in Data Science - Thesis on measuring the impact of DevRel in the sustainability of OSS Communities [email protected] DevRel Foundation
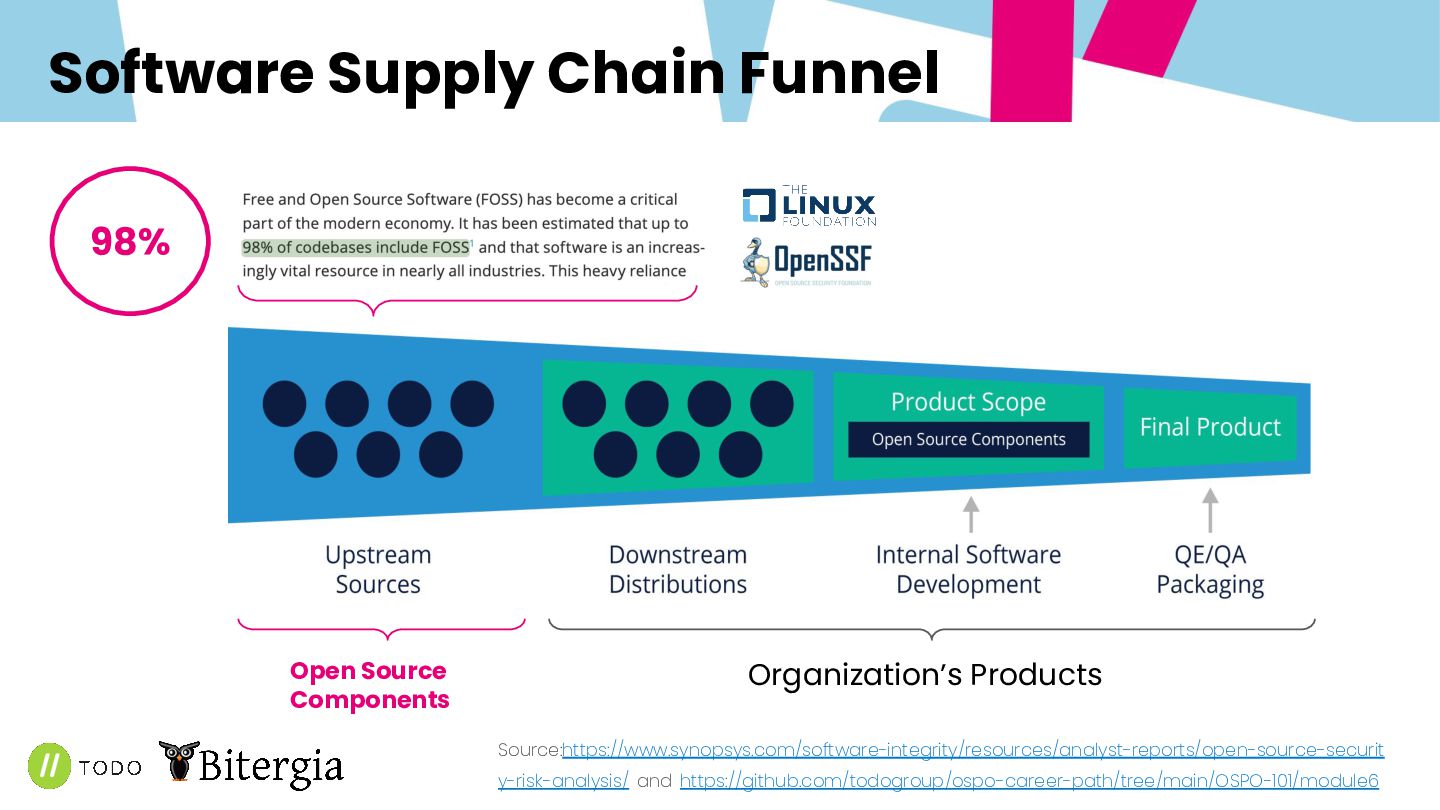
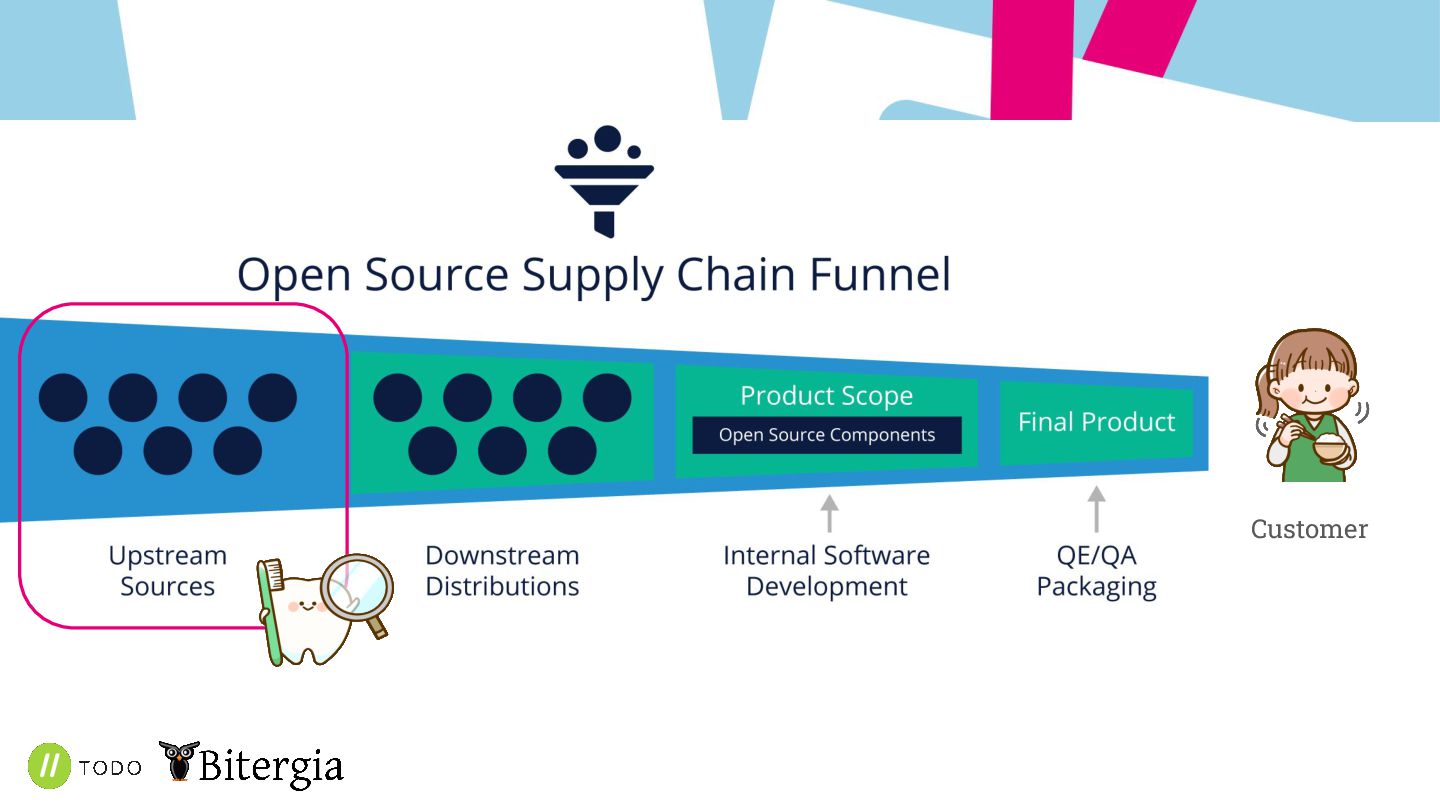
Source:https://www.synopsys.com/software-integrity/resources/analyst-reports/open-source-securit y-risk-analysis/ and https://github.com/todogroup/ospo-career-path/tree/main/OSPO-101/module6
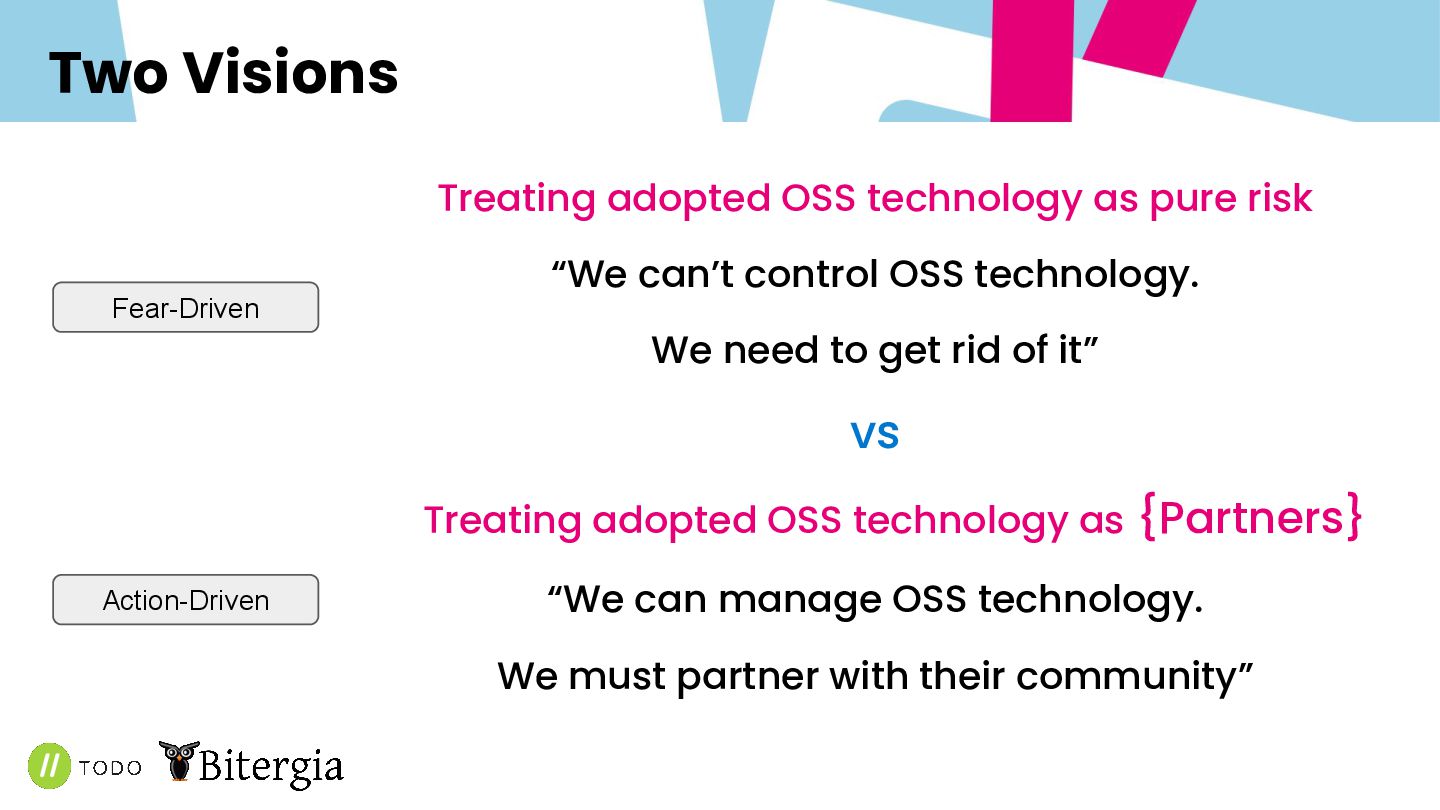
OSS technology. We need to get rid of it” vs Treating adopted OSS technology as {Partners} “We can manage OSS technology. We must partner with their community” Two Visions Fear-Driven Action-Driven
Industry Risk management strategies differ across industries, with varying importance placed on different variables. By Size Large organizations face unique challenges in risk identification and prioritization. What is my orgs ROI?
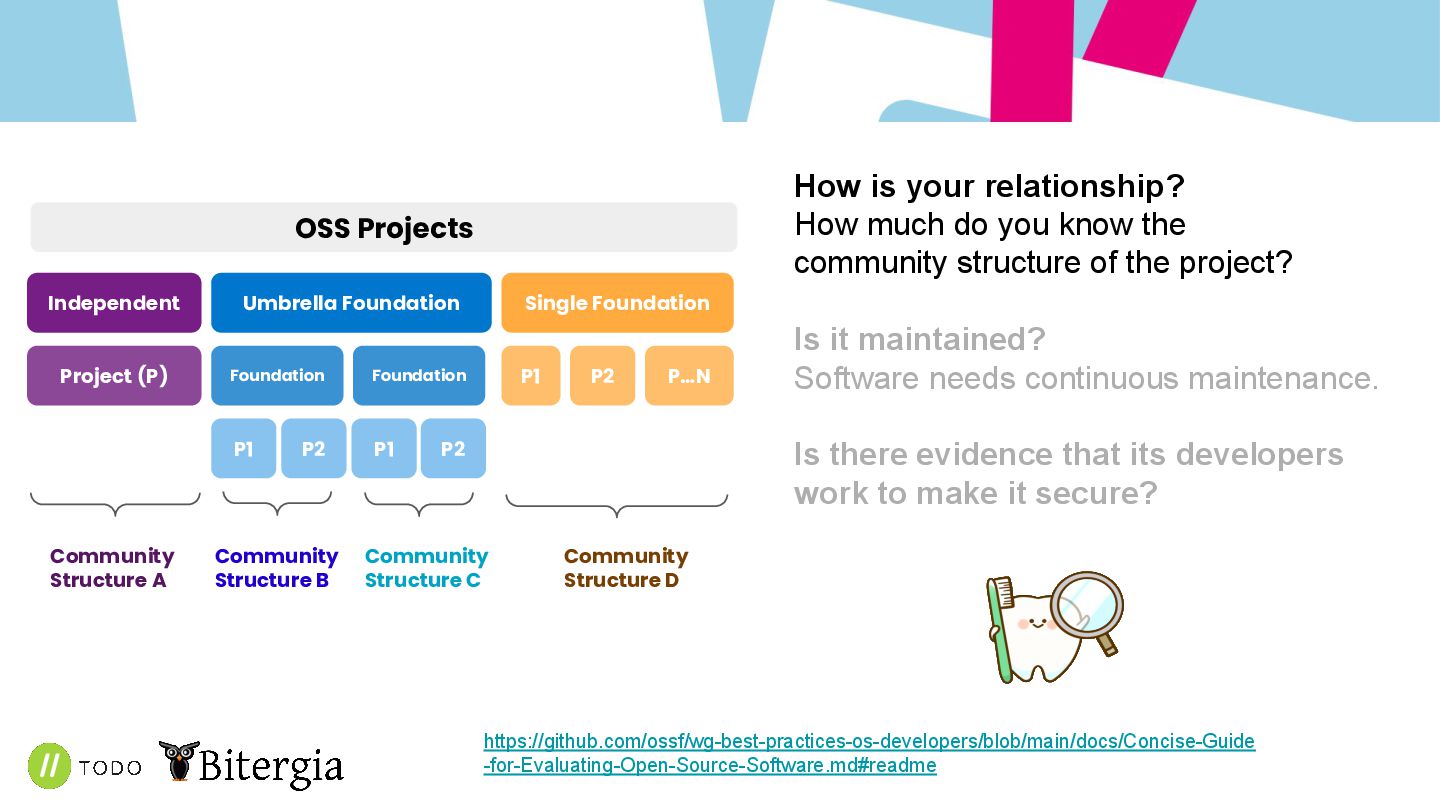
community structure of the project? Is it maintained? Software needs continuous maintenance. Is there evidence that its developers work to make it secure? https://github.com/ossf/wg-best-practices-os-developers/blob/main/docs/Concise-Guide -for-Evaluating-Open-Source-Software.md#readme OSS Projects Independent Umbrella Foundation Single Foundation Foundation Project (P) P1 P2 P…N P1 P2 Foundation P1 P2 Community Structure A Community Structure B Community Structure C Community Structure D
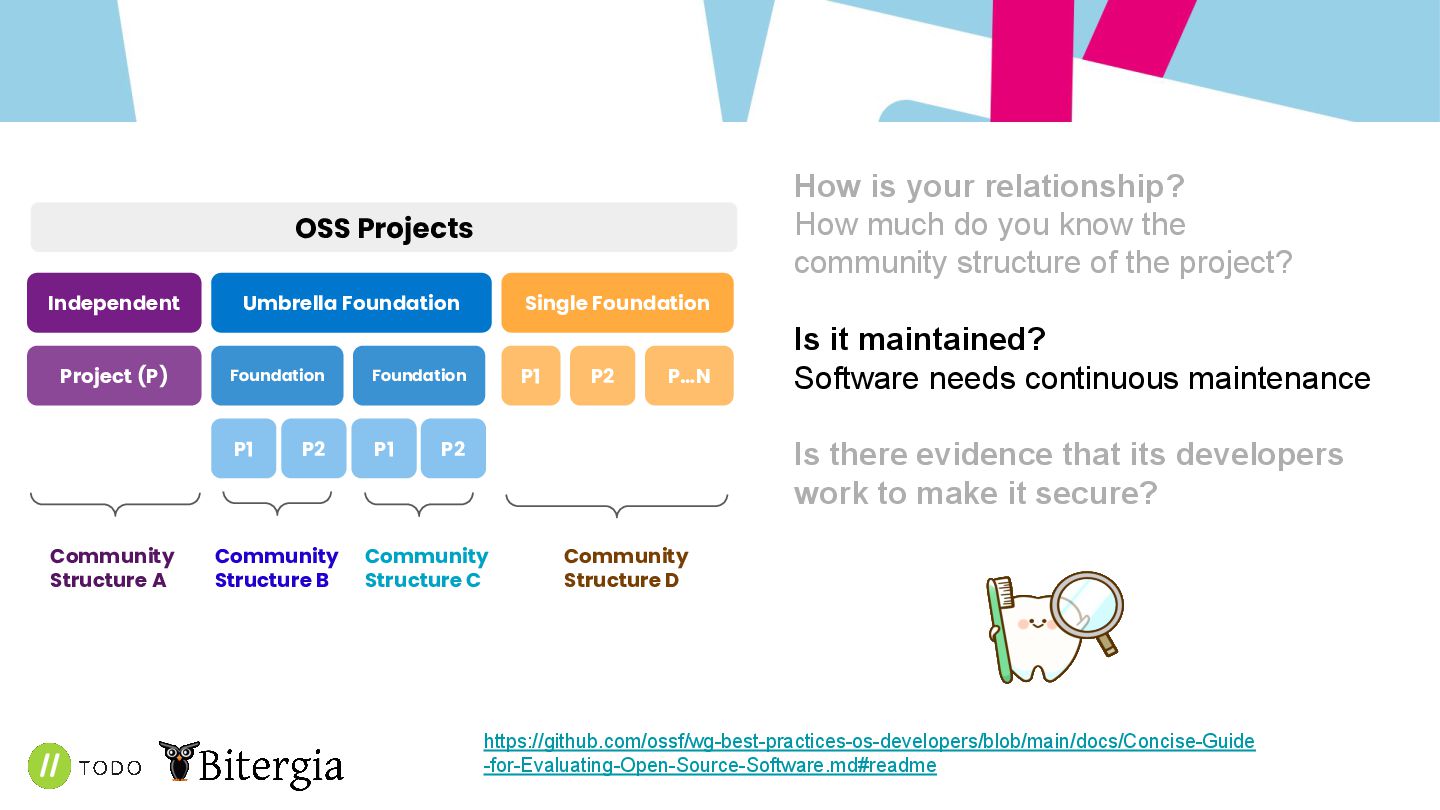
community structure of the project? Is it maintained? Software needs continuous maintenance Is there evidence that its developers work to make it secure? https://github.com/ossf/wg-best-practices-os-developers/blob/main/docs/Concise-Guide -for-Evaluating-Open-Source-Software.md#readme OSS Projects Independent Umbrella Foundation Single Foundation Foundation Project (P) P1 P2 P…N P1 P2 Foundation P1 P2 Community Structure A Community Structure B Community Structure C Community Structure D
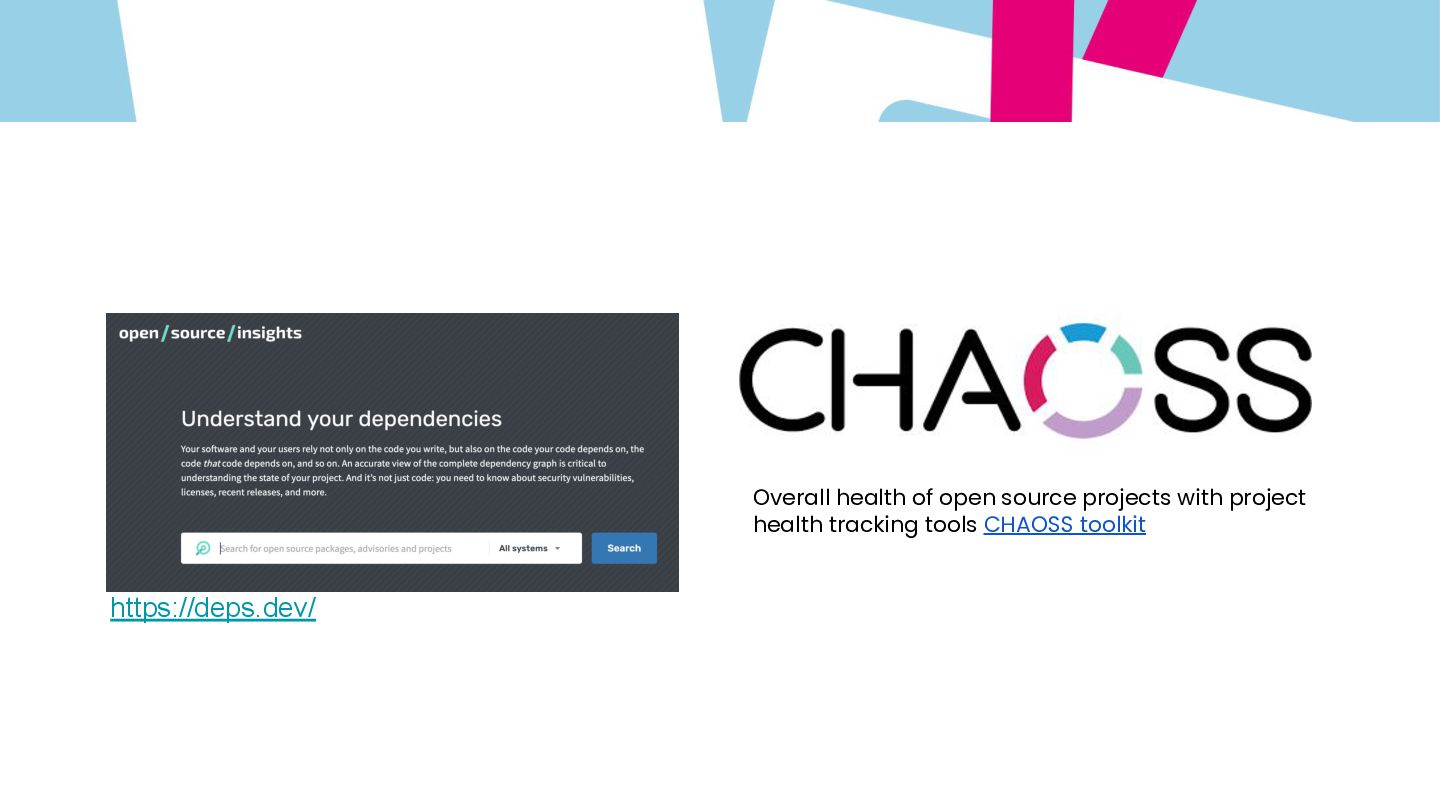
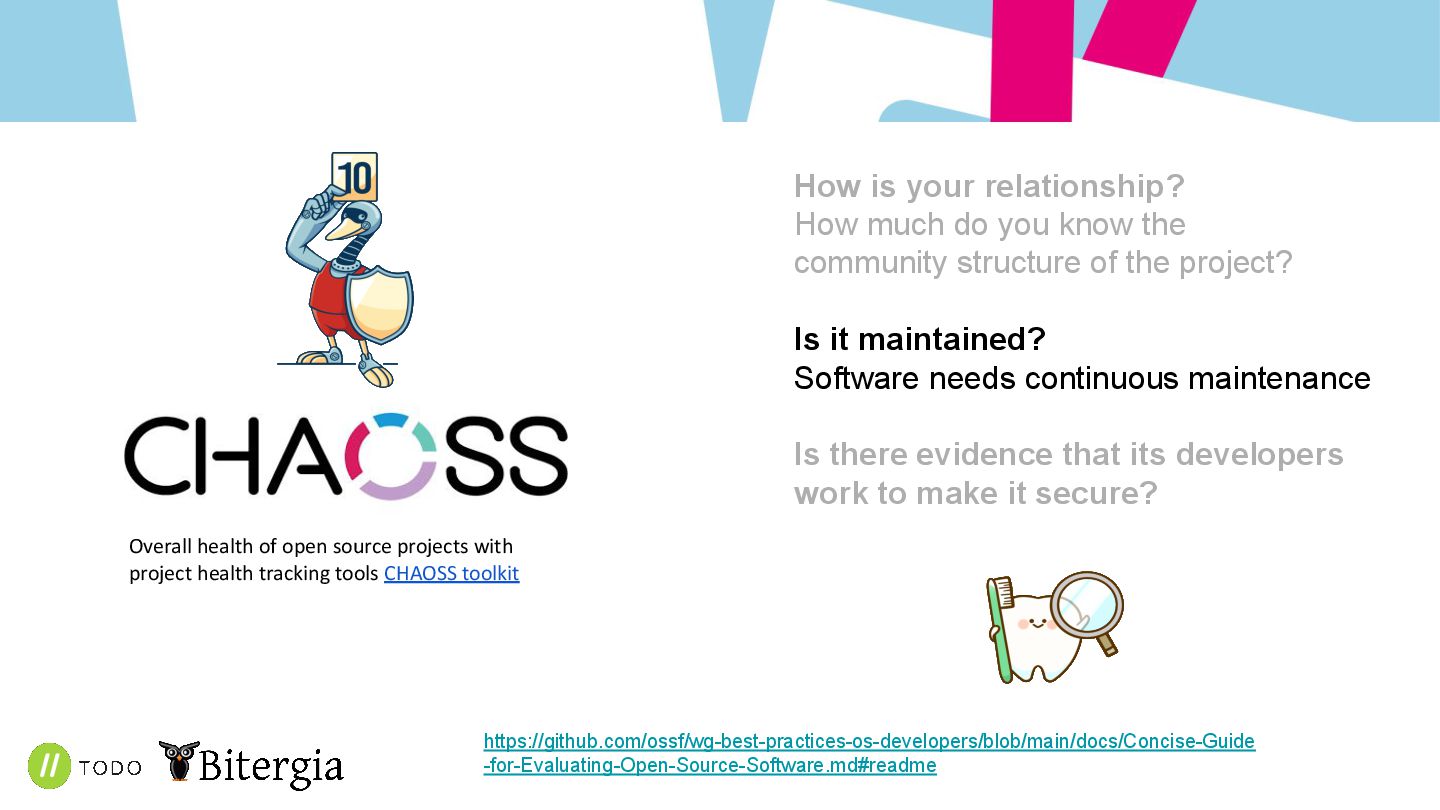
community structure of the project? Is it maintained? Software needs continuous maintenance Is there evidence that its developers work to make it secure? https://github.com/ossf/wg-best-practices-os-developers/blob/main/docs/Concise-Guide -for-Evaluating-Open-Source-Software.md#readme Overall health of open source projects with project health tracking tools CHAOSS toolkit
tools CHAOSS toolkit How is your relationship? How much do you know the community structure of the project? Is it maintained? Software needs continuous maintenance. Is there evidence that its developers work to make it secure? https://github.com/ossf/wg-best-practices-os-developers/blob/main/docs/Concise-Guide -for-Evaluating-Open-Source-Software.md#readme
important in software development • Key things managers of software developers must do • Introduction to security concepts • Applying security to your projects
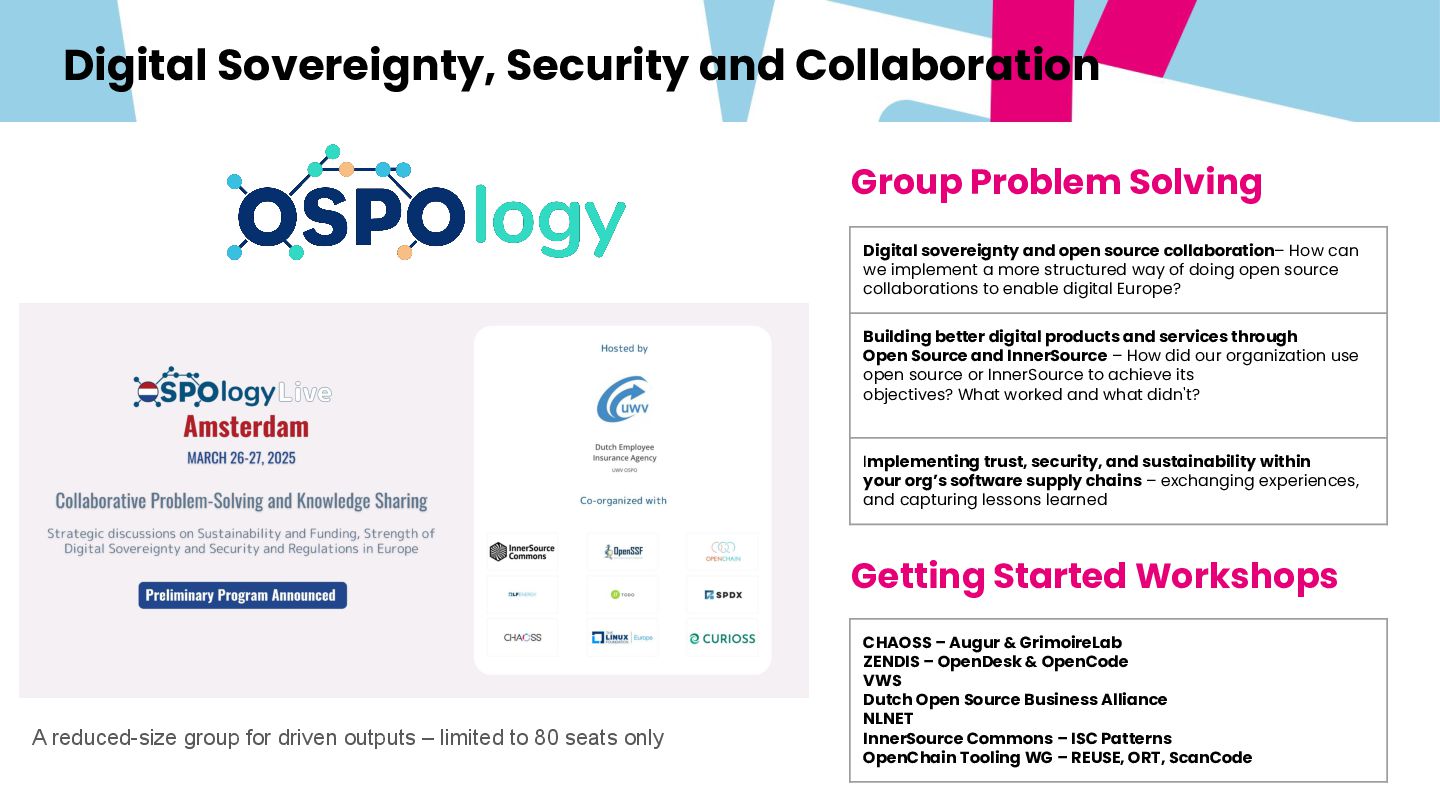
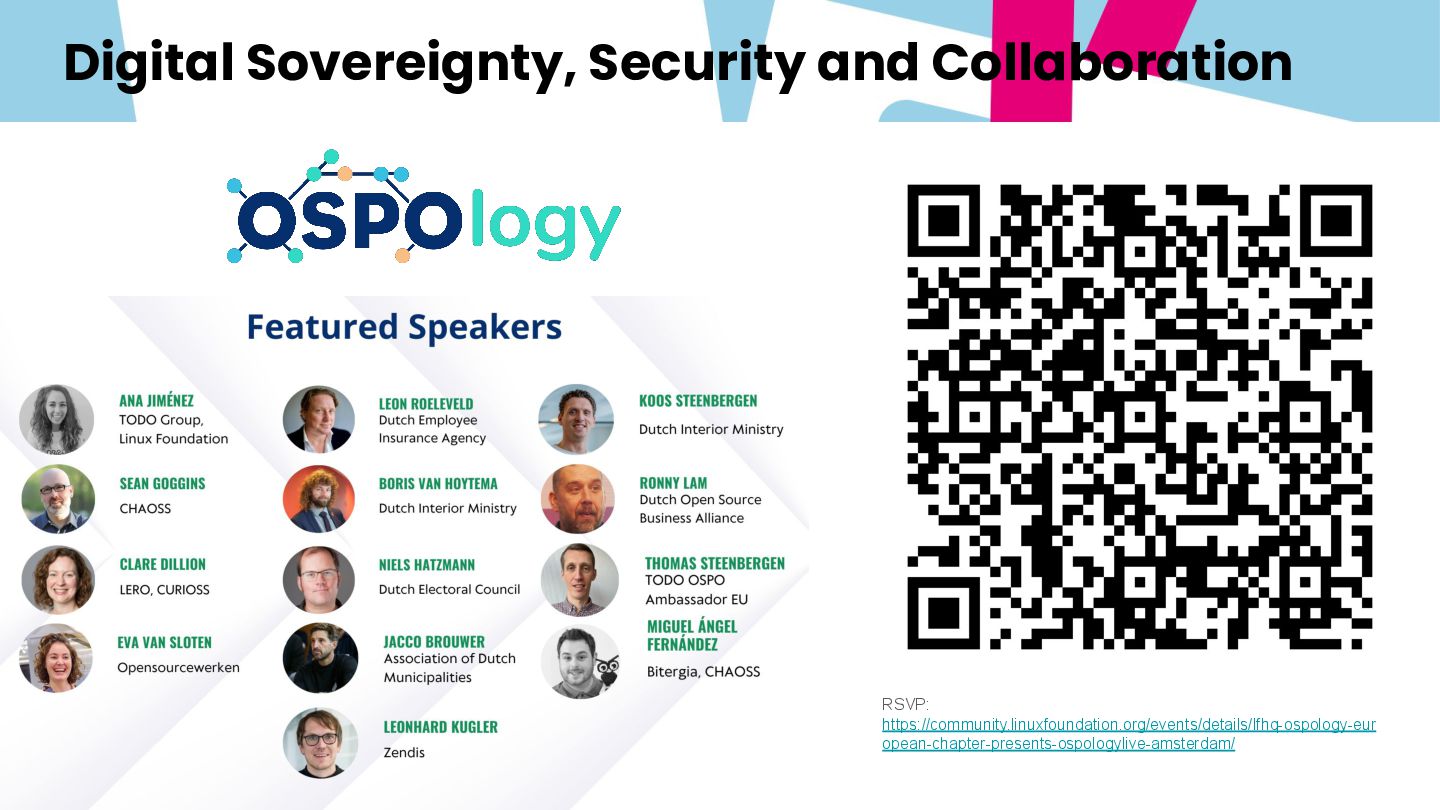
collaboration– How can we implement a more structured way of doing open source collaborations to enable digital Europe? Building better digital products and services through Open Source and InnerSource – How did our organization use open source or InnerSource to achieve its objectives? What worked and what didn't? Implementing trust, security, and sustainability within your org’s software supply chains – exchanging experiences, and capturing lessons learned Group Problem Solving CHAOSS – Augur & GrimoireLab ZENDIS – OpenDesk & OpenCode VWS Dutch Open Source Business Alliance NLNET InnerSource Commons – ISC Patterns OpenChain Tooling WG – REUSE, ORT, ScanCode Getting Started Workshops A reduced-size group for driven outputs – limited to 80 seats only
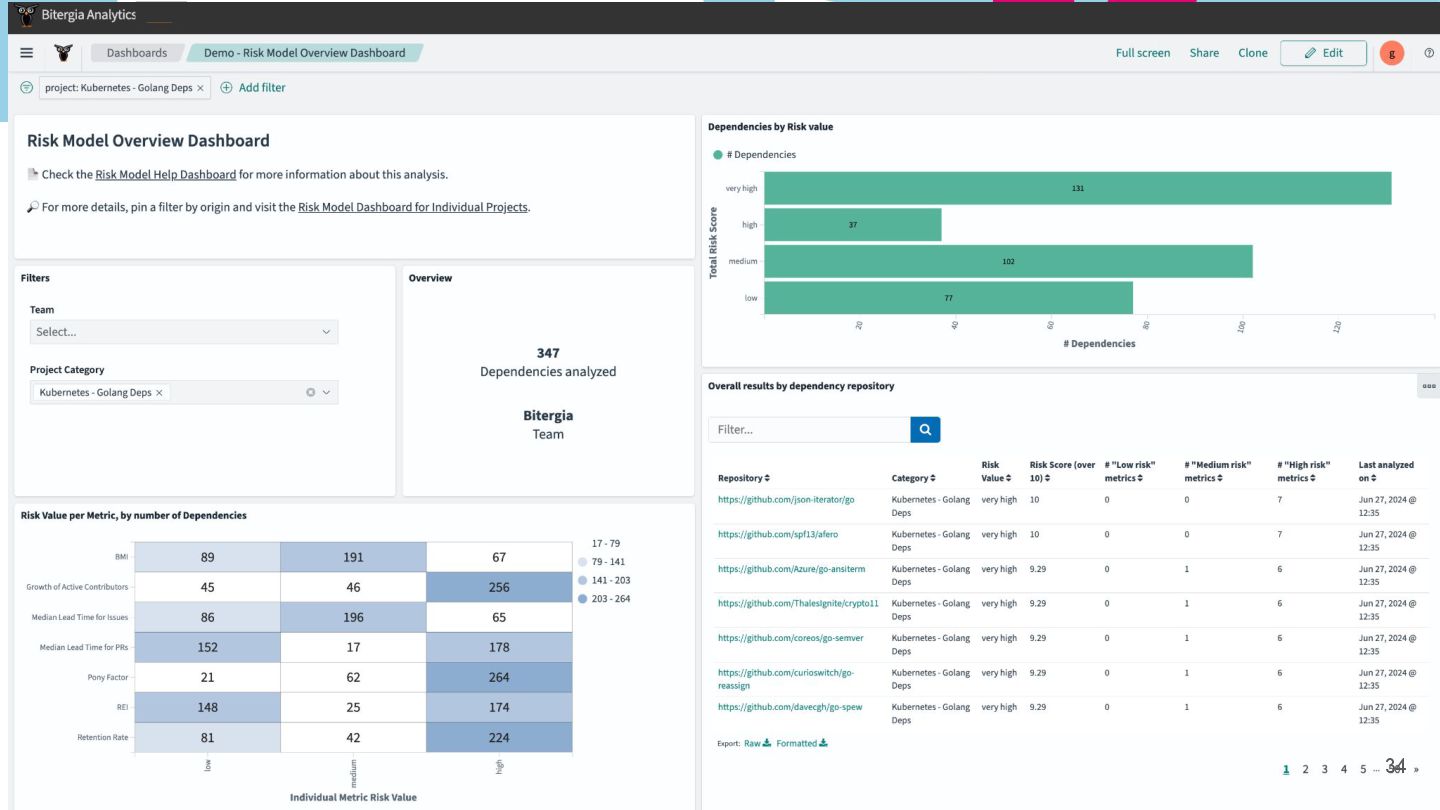
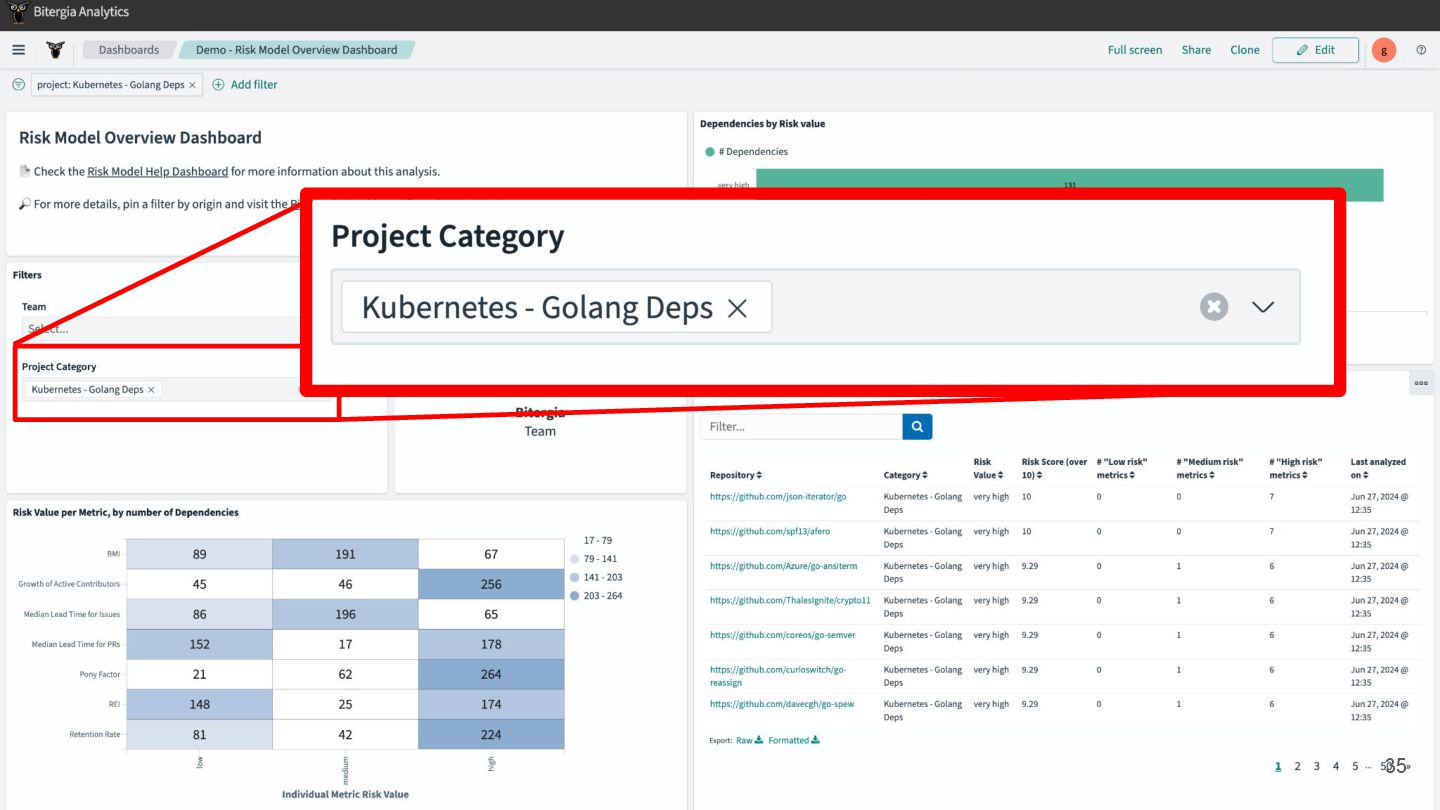
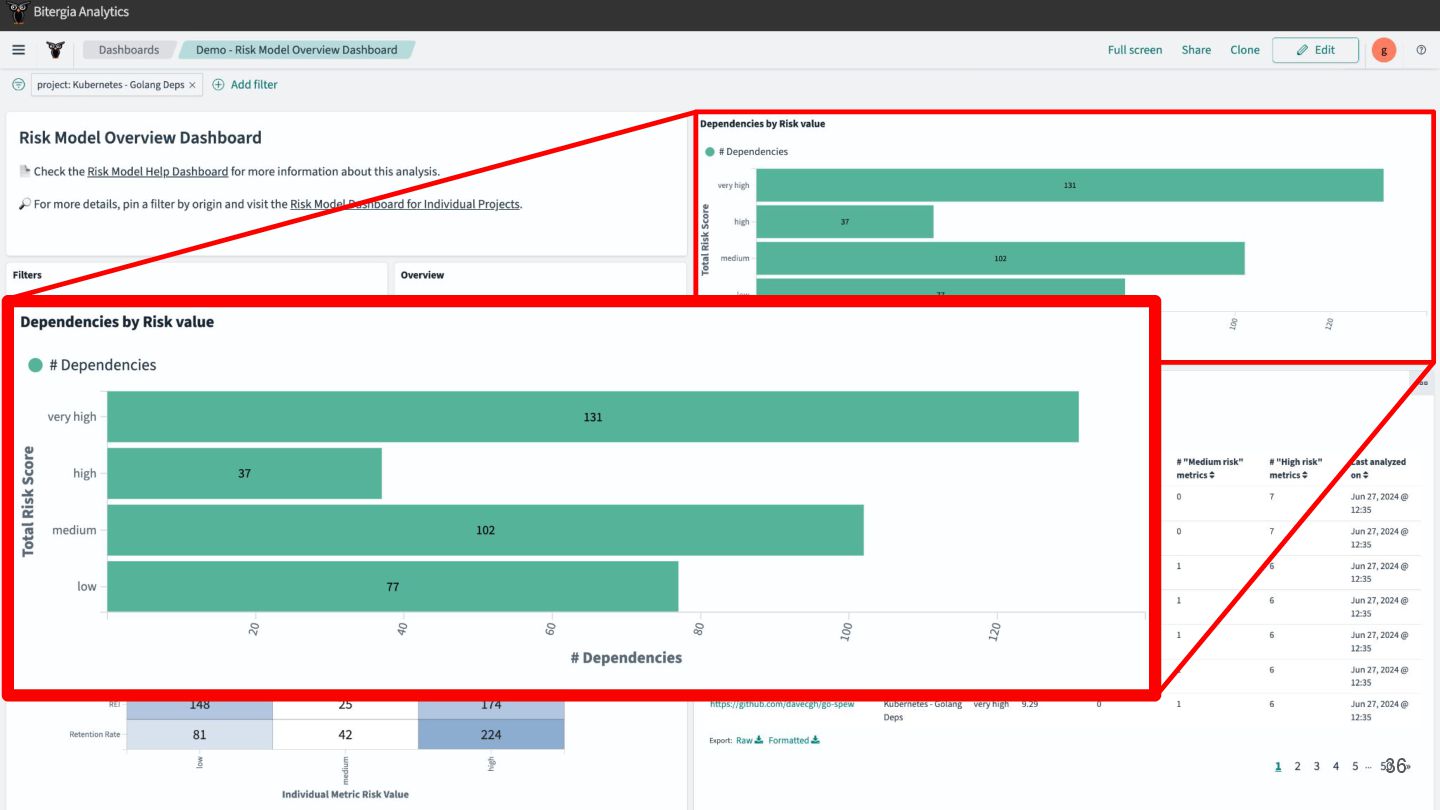
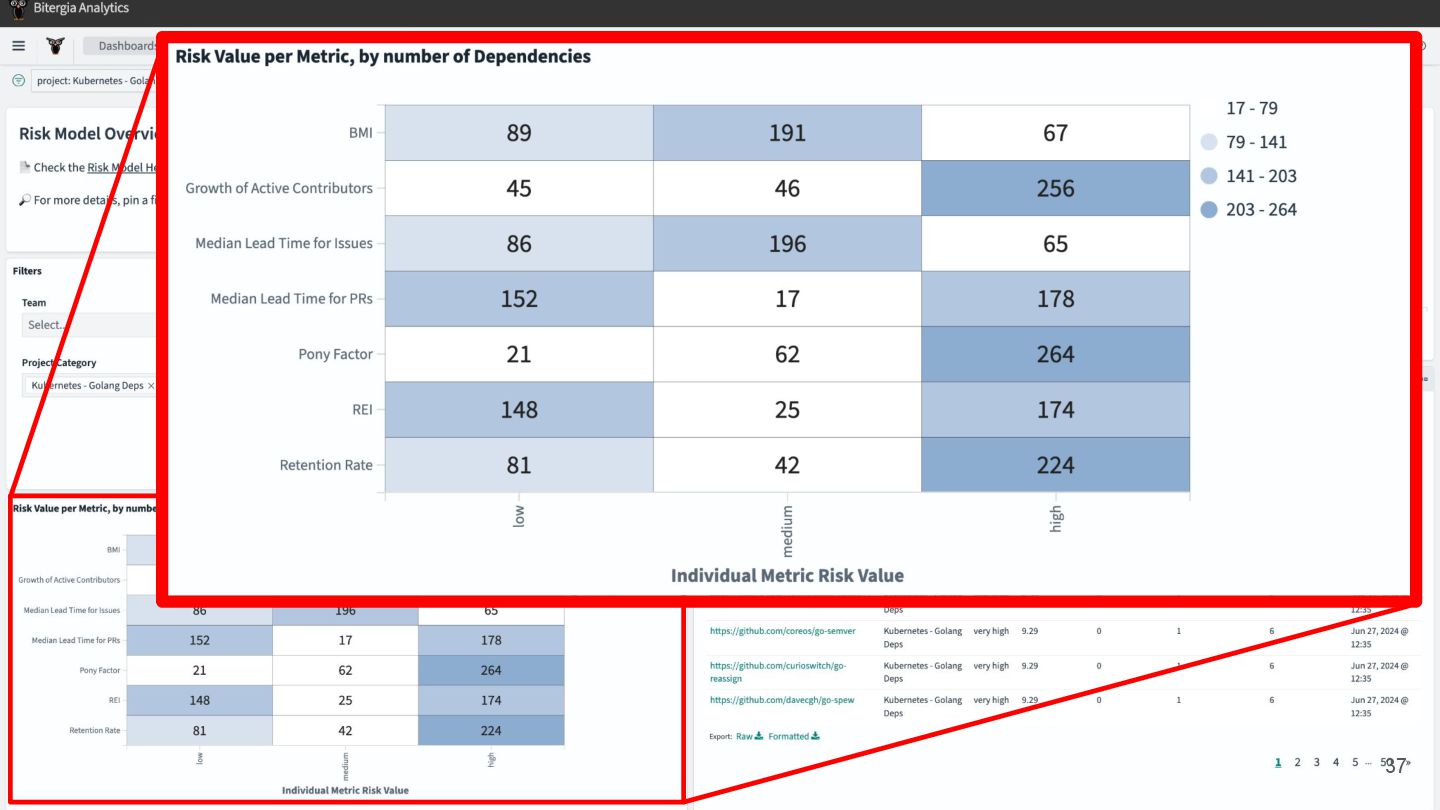
• Community cannot handle workload ◦ Backlog Management Index ◦ Review Efficiency Index • Community does not address work quickly ◦ Median Lead Time for Issues ◦ Median Lead Time for Pull Requests • Community lacks sufficient talent ◦ Retention Rate ◦ Growth of Active Contributors ◦ Contributor Absence Factor (aka Bus or Pony Factor)
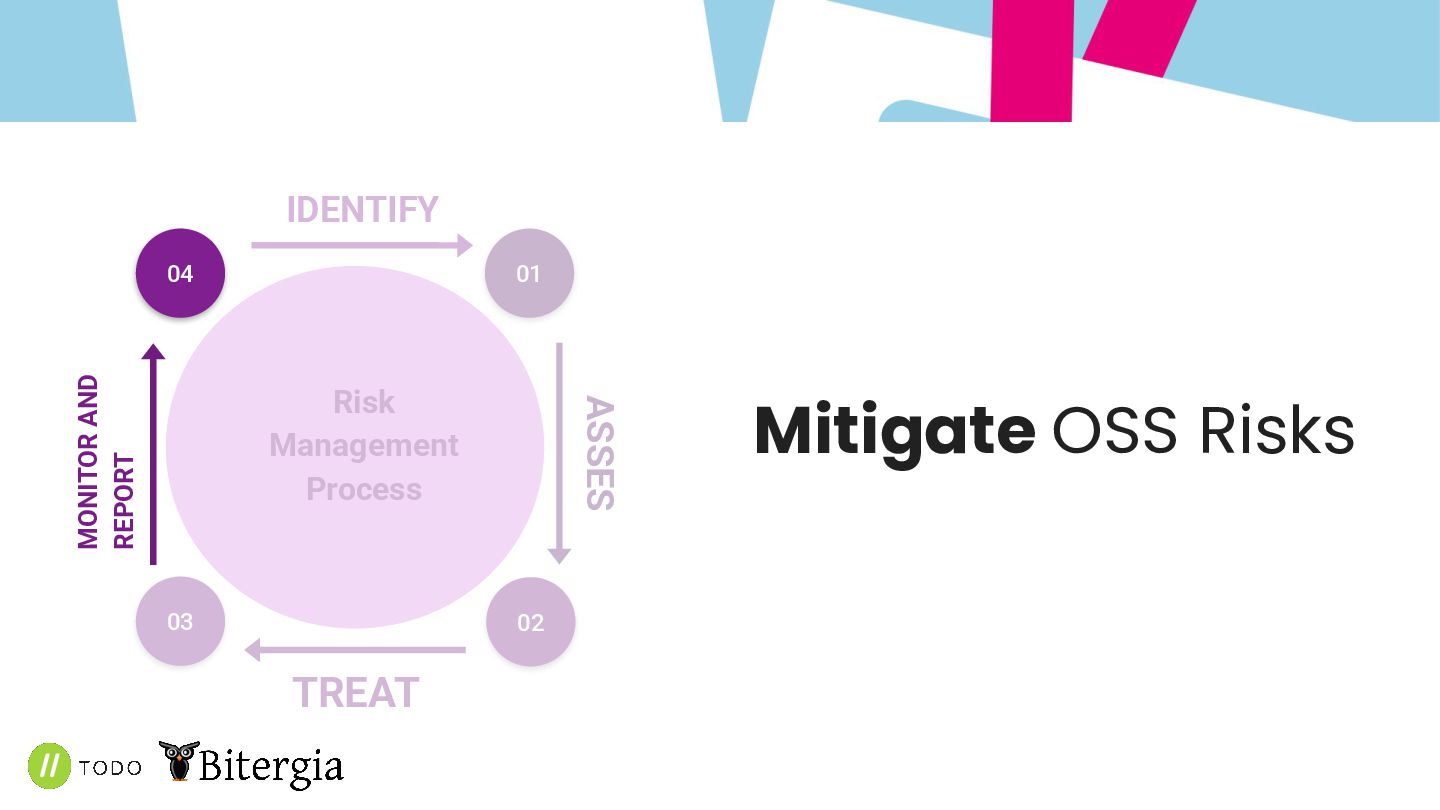
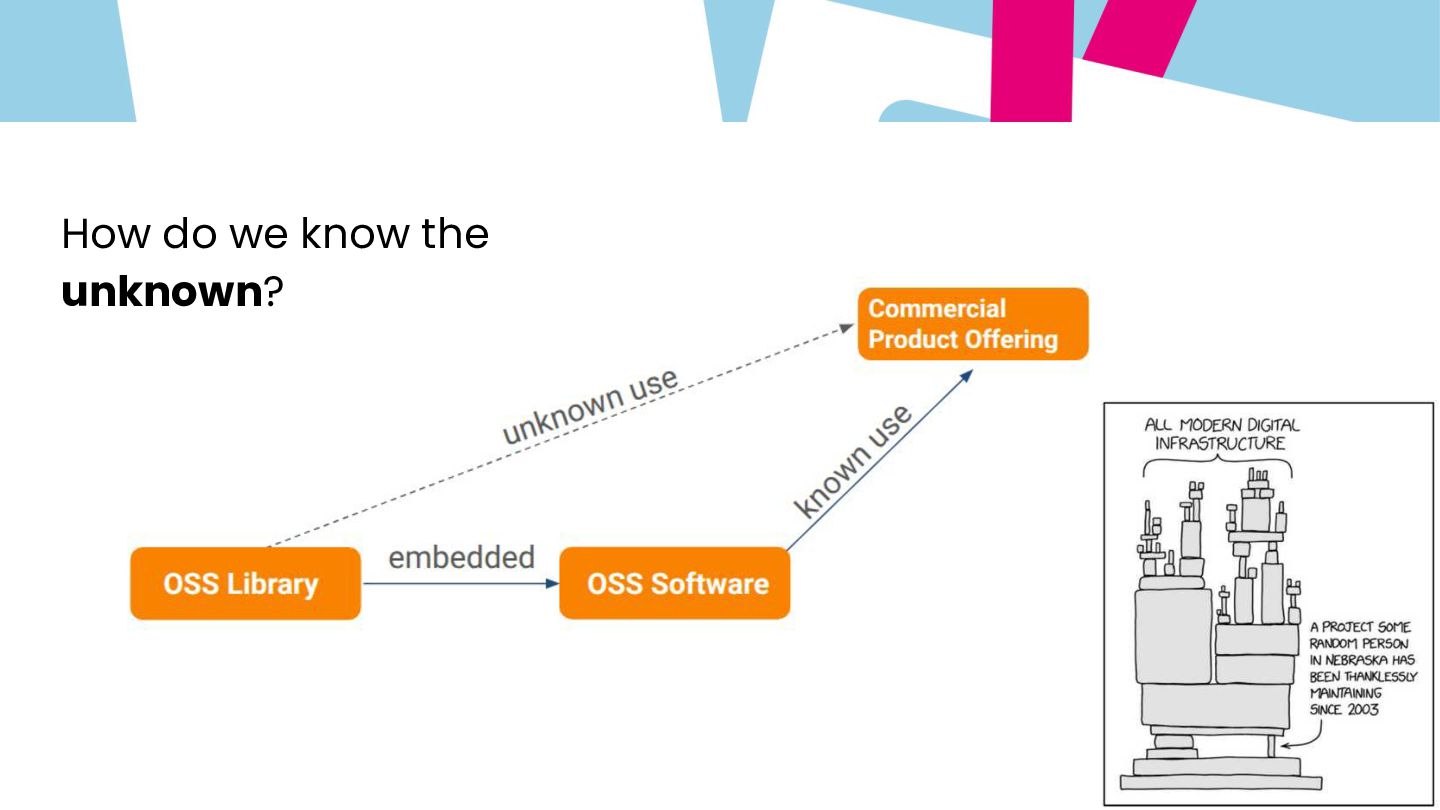
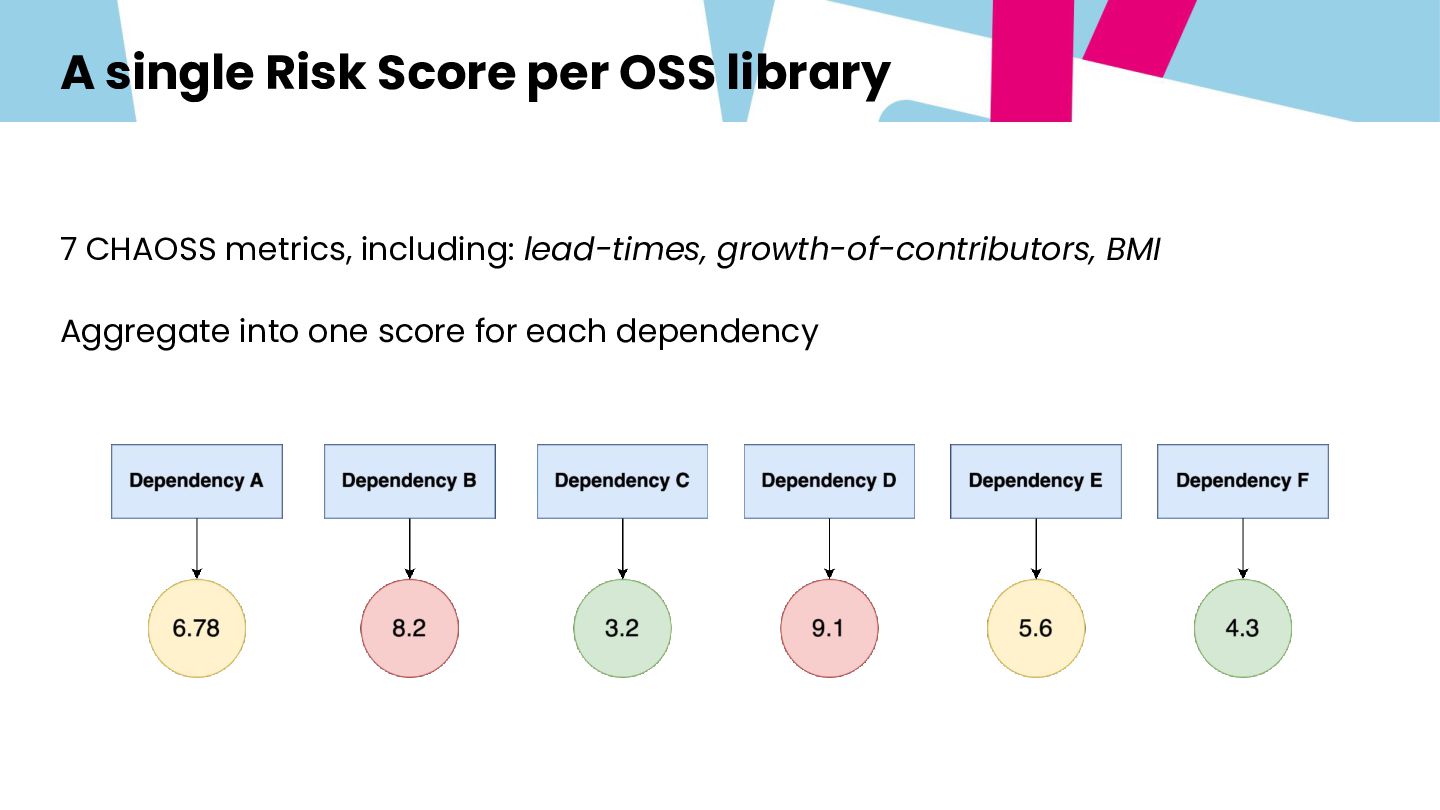
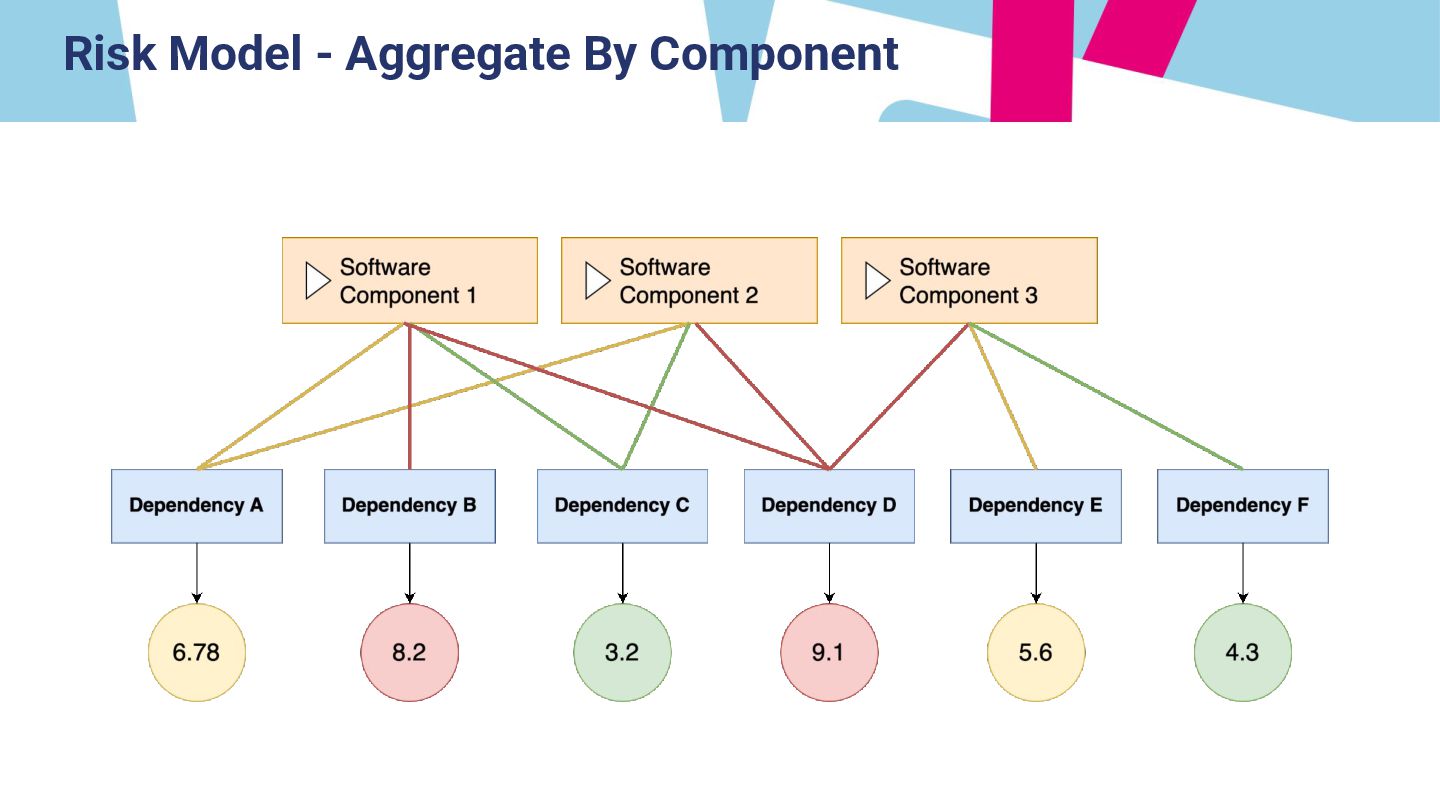
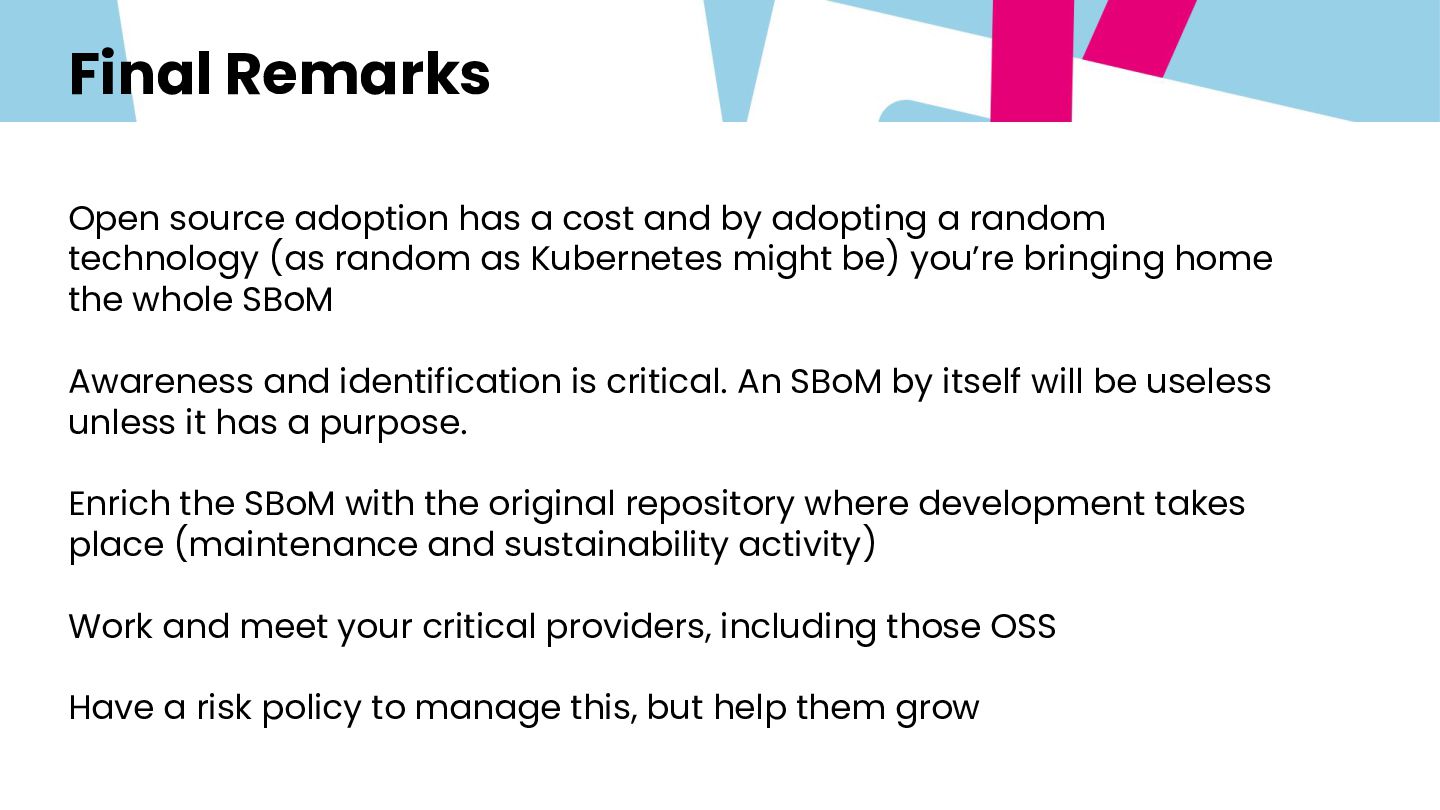
adopting a random technology (as random as Kubernetes might be) you’re bringing home the whole SBoM Awareness and identification is critical. An SBoM by itself will be useless unless it has a purpose. Enrich the SBoM with the original repository where development takes place (maintenance and sustainability activity) Work and meet your critical providers, including those OSS Have a risk policy to manage this, but help them grow


 anajsana
 smartcamp
 kgnkhkr
 smartgate
 fado_dev
 natty_natty254
 kotasugiki
 chibanba1982
 flux
 loglass2019
 sekithermal
 circulation
 colly
 varn
 holman
 codingconduct
 speakerdeck
 frankvandijk
 carmenintech
 jakevdp
 baasie
 reverentgeek
 garrettdimon
 honzajavorek