Upgrade to Pro — share decks privately, control downloads, hide ads and more …

DevOps for the Rubyist Soul at Steel City Ruby ...

DevOps for the Rubyist Soul at Steel City Ruby 2013

John Downey

August 17, 2013

Transcript

114 slides
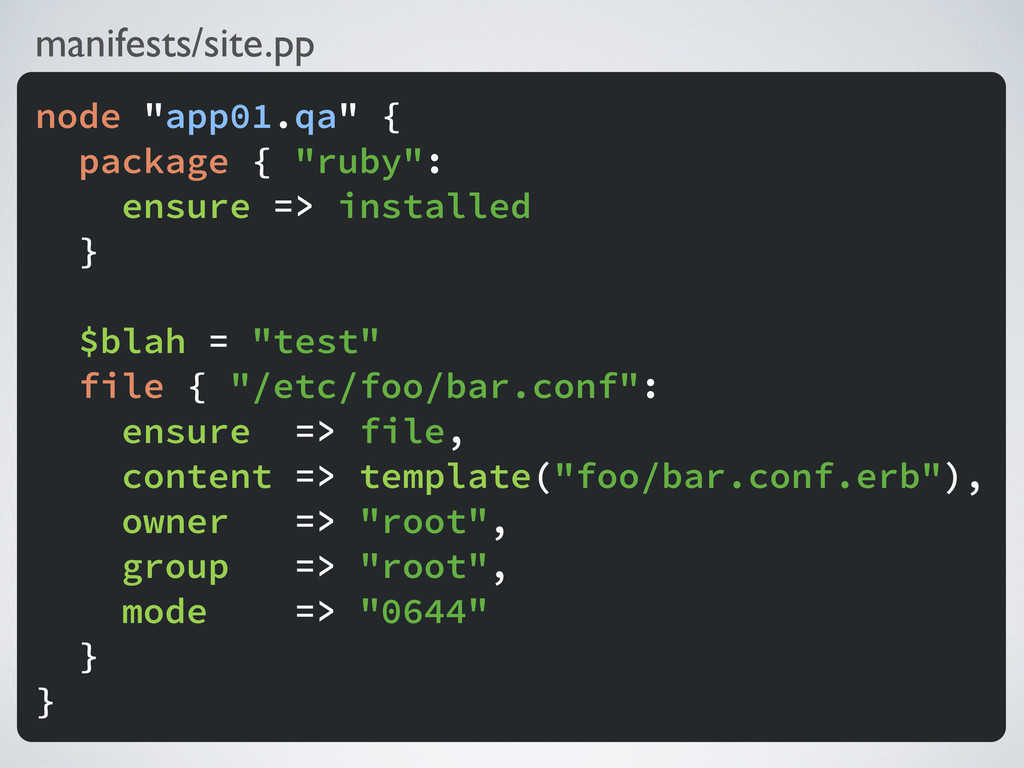
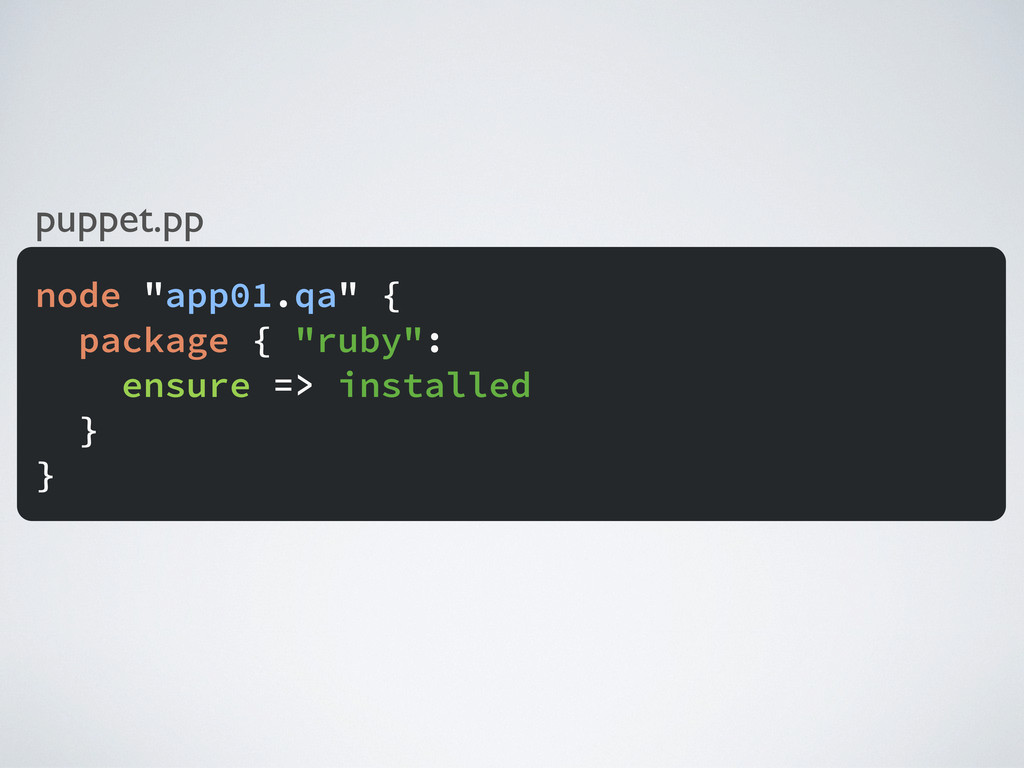
  1. manifests/site.pp node "app01.qa" { package { "ruby": ensure => installed

    } $blah = "test" file { "/etc/foo/bar.conf": ensure => file, content => template("foo/bar.conf.erb"), owner => "root", group => "root", mode => "0644" } }
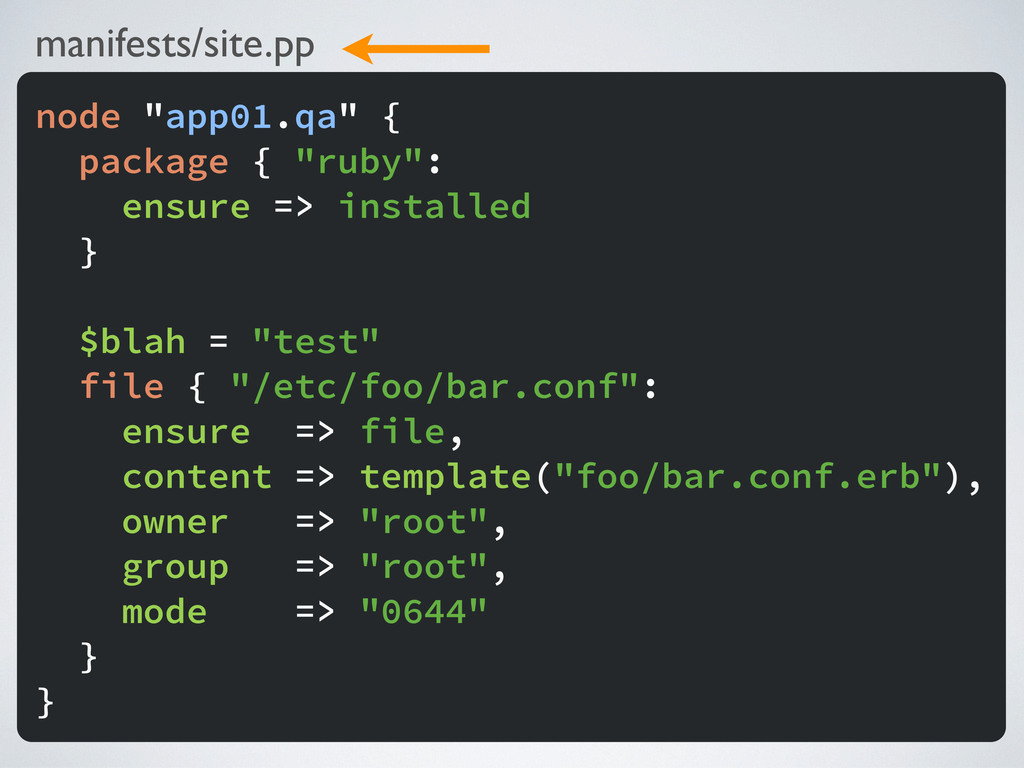
  2. manifests/site.pp node "app01.qa" { package { "ruby": ensure => installed

    } $blah = "test" file { "/etc/foo/bar.conf": ensure => file, content => template("foo/bar.conf.erb"), owner => "root", group => "root", mode => "0644" } }
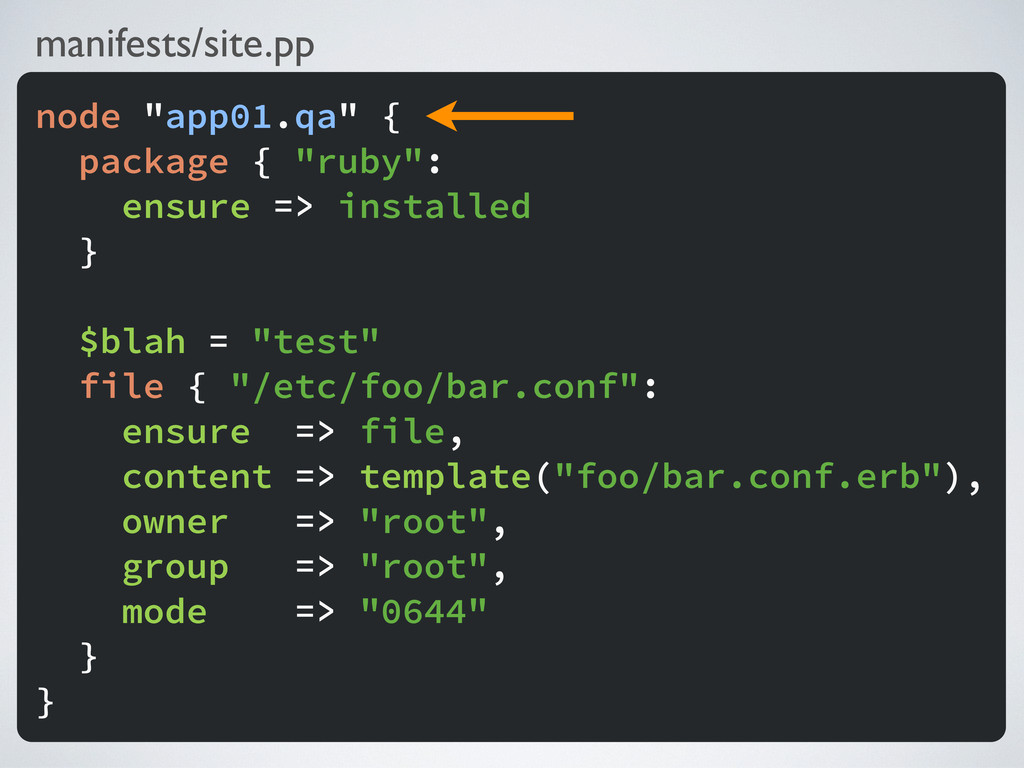
  3. manifests/site.pp node "app01.qa" { package { "ruby": ensure => installed

    } $blah = "test" file { "/etc/foo/bar.conf": ensure => file, content => template("foo/bar.conf.erb"), owner => "root", group => "root", mode => "0644" } }
  4. manifests/site.pp node "app01.qa" { package { "ruby": ensure => installed

    } $blah = "test" file { "/etc/foo/bar.conf": ensure => file, content => template("foo/bar.conf.erb"), owner => "root", group => "root", mode => "0644" } }
  5. manifests/site.pp node "app01.qa" { package { "ruby": ensure => installed

    } $blah = "test" file { "/etc/foo/bar.conf": ensure => file, content => template("foo/bar.conf.erb"), owner => "root", group => "root", mode => "0644" } }
  6. manifests/site.pp node "app01.qa" { package { "ruby": ensure => installed

    } $blah = "test" file { "/etc/foo/bar.conf": ensure => file, content => template("foo/bar.conf.erb"), owner => "root", group => "root", mode => "0644" } }
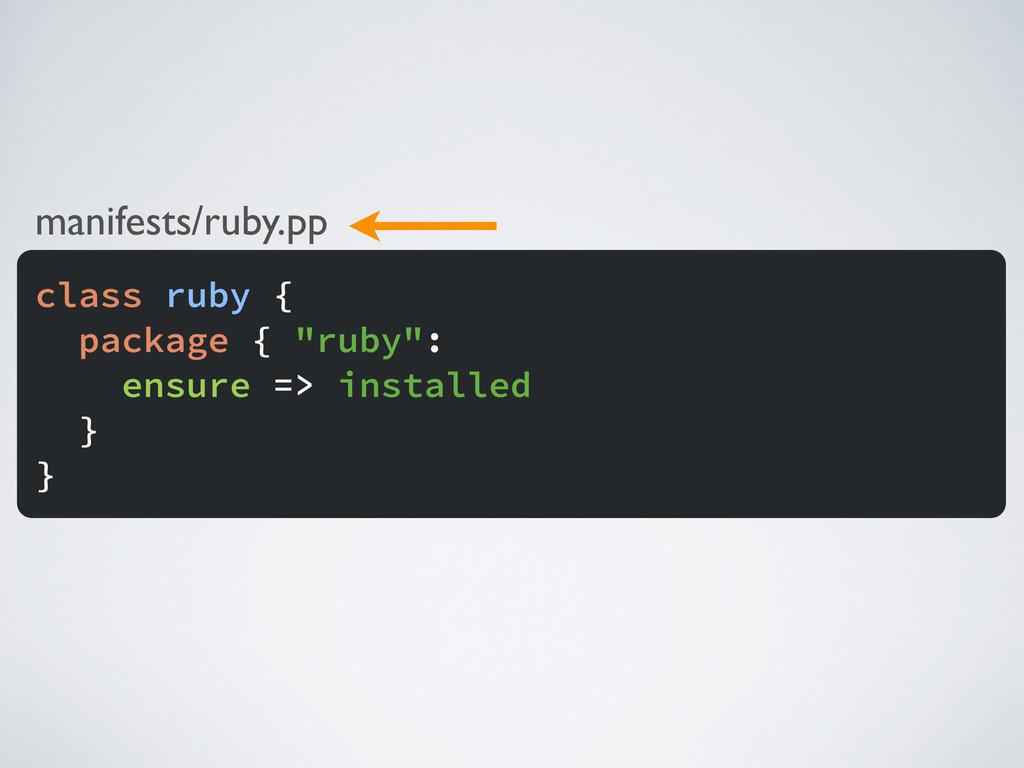
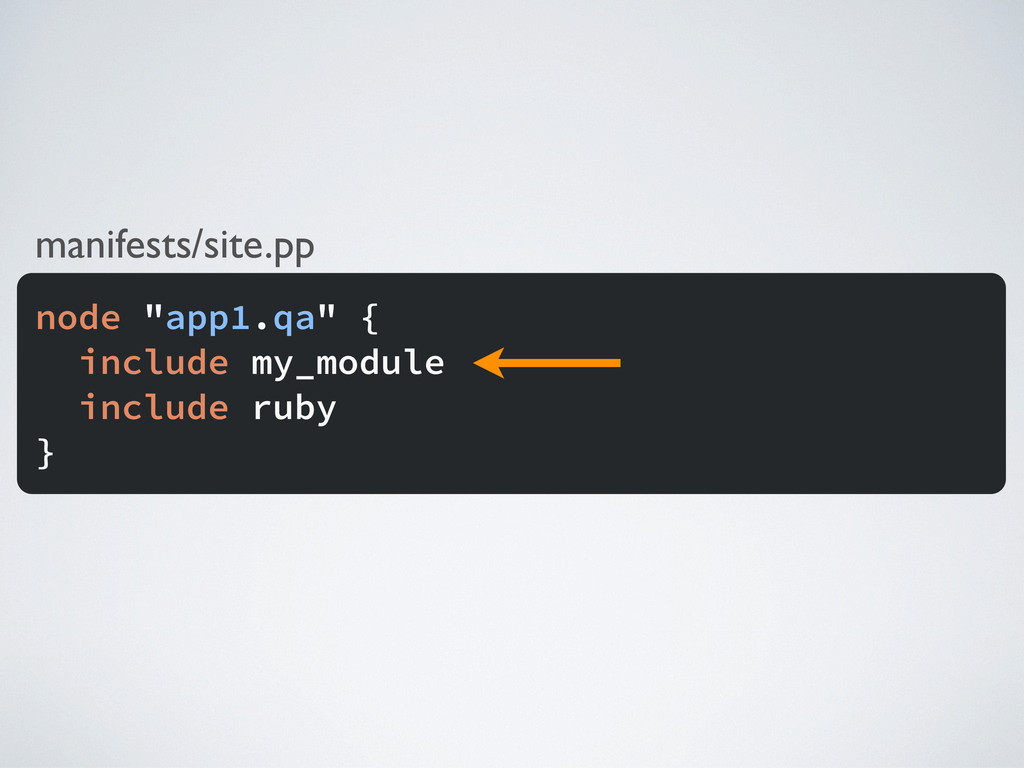
  7. manifests/site.pp node "app1.qa" { include ruby $blah = "test" file

    { "/etc/foo/bar.conf": ensure => file, content => template("foo/bar.conf.erb"), owner => "root", group => "root", mode => "0644" } }
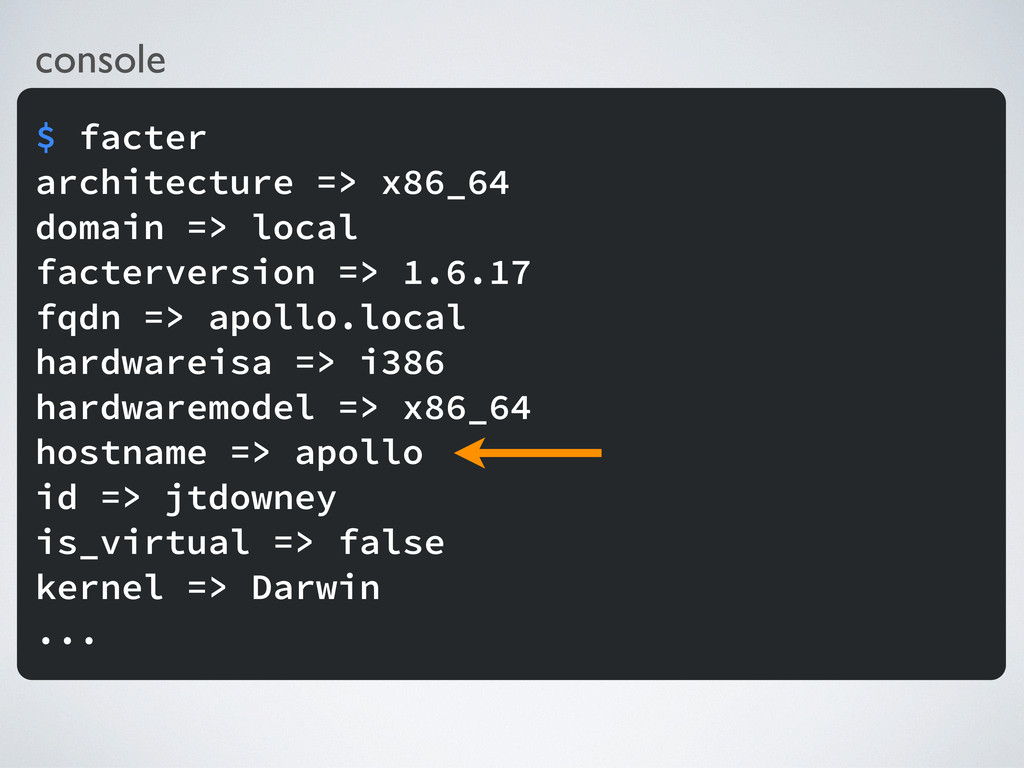
  8. console $ facter architecture => x86_64 domain => local facterversion

    => 1.6.17 fqdn => apollo.local hardwareisa => i386 hardwaremodel => x86_64 hostname => apollo id => jtdowney is_virtual => false kernel => Darwin ...
  9. console $ facter architecture => x86_64 domain => local facterversion

    => 1.6.17 fqdn => apollo.local hardwareisa => i386 hardwaremodel => x86_64 hostname => apollo id => jtdowney is_virtual => false kernel => Darwin ...
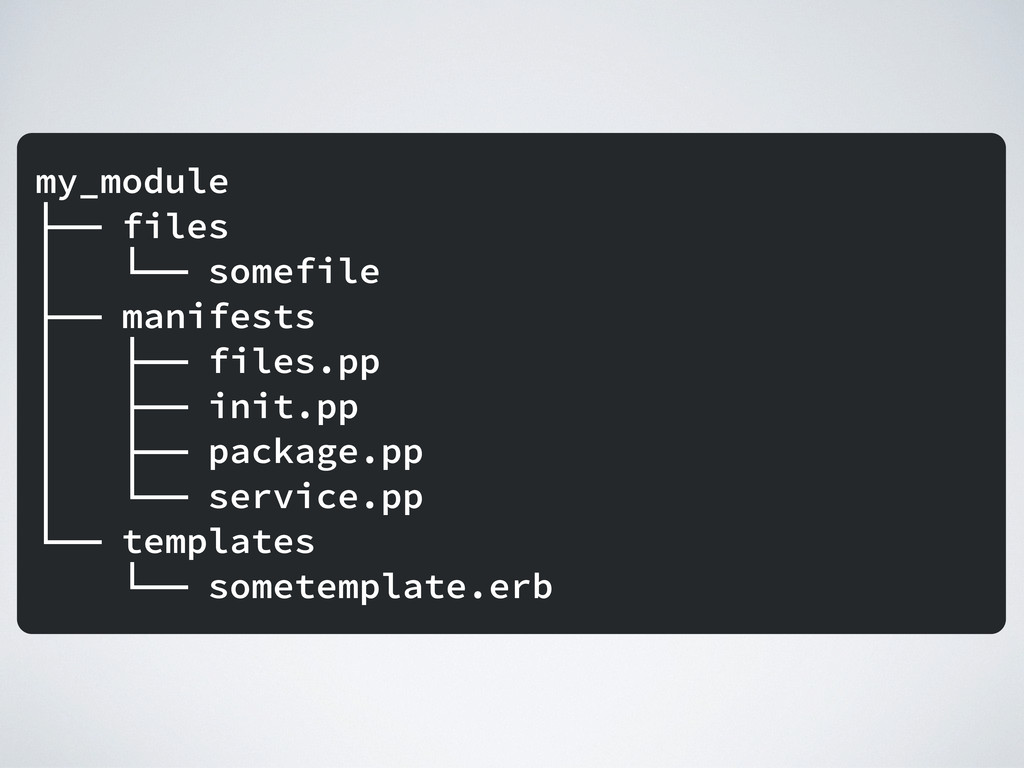
  10. my_module ├── files │ └── somefile ├── manifests │ ├──

    files.pp │ ├── init.pp │ ├── package.pp │ └── service.pp └── templates └── sometemplate.erb
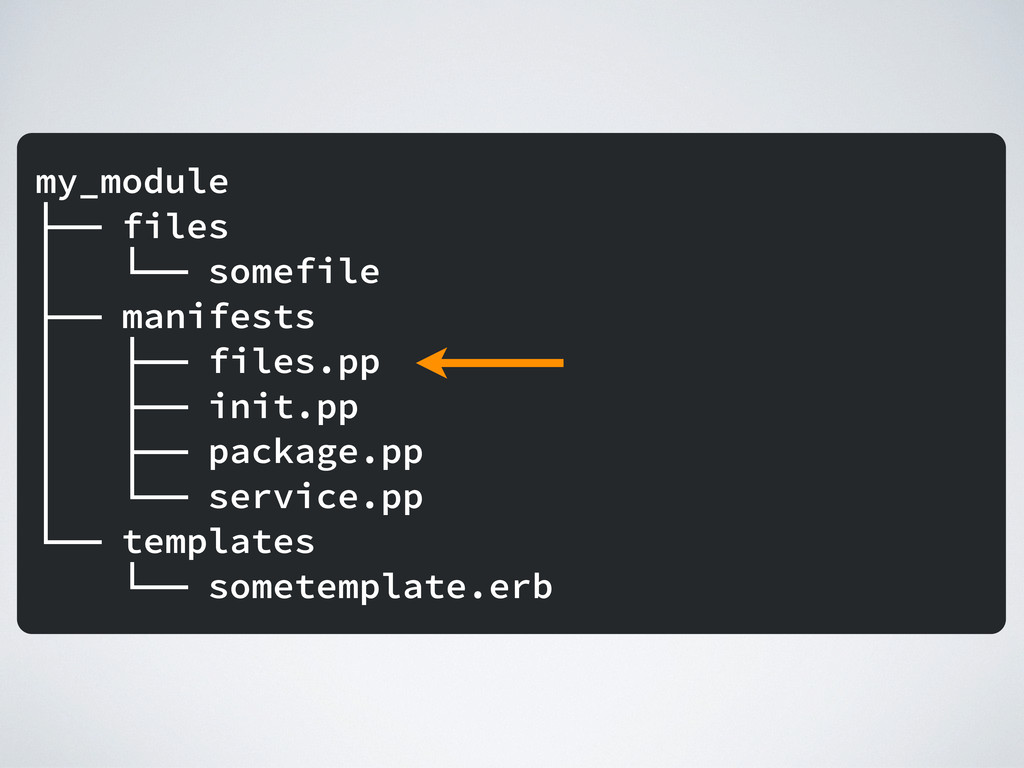
  11. my_module ├── files │ └── somefile ├── manifests │ ├──

    files.pp │ ├── init.pp │ ├── package.pp │ └── service.pp └── templates └── sometemplate.erb
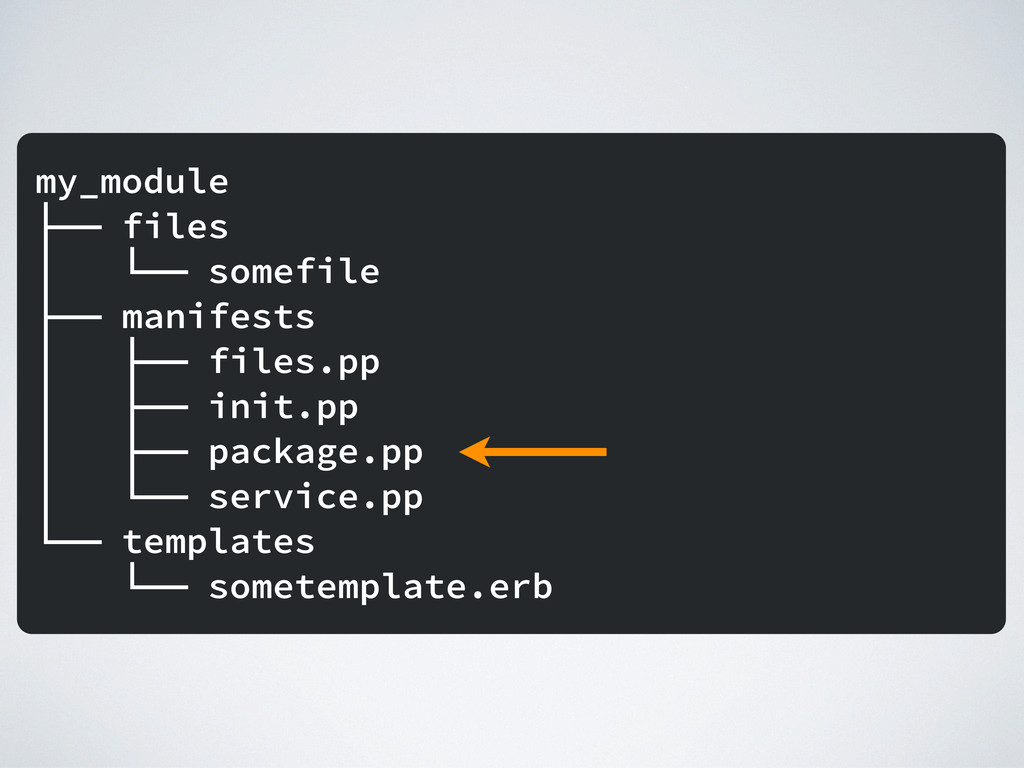
  12. my_module ├── files │ └── somefile ├── manifests │ ├──

    files.pp │ ├── init.pp │ ├── package.pp │ └── service.pp └── templates └── sometemplate.erb
  13. my_module ├── files │ └── somefile ├── manifests │ ├──

    files.pp │ ├── init.pp │ ├── package.pp │ └── service.pp └── templates └── sometemplate.erb
  14. my_module ├── files │ └── somefile ├── manifests │ ├──

    files.pp │ ├── init.pp │ ├── package.pp │ └── service.pp └── templates └── sometemplate.erb
  15. my_module ├── files │ └── somefile ├── manifests │ ├──

    files.pp │ ├── init.pp │ ├── package.pp │ └── service.pp └── templates └── sometemplate.erb
  16. Puppet does not manage truth, puppet maps truth to complexity

    http://www.flickr.com/photos/brionybarr/4310798716/
  17. modules/nagios/manifests/init.pp class nagios::init { $servers = ["proxy1.qa", "proxy2.qa"] file {

    "/etc/nagios3/host-proxy.conf": ensure => file, content => template("nagios/proxy.erb"), owner => "root", group => "root", mode => "0644" } }
  18. modules/nagios/manifests/init.pp class nagios::init { $servers = ["proxy1.qa", "proxy2.qa"] file {

    "/etc/nagios3/host-proxy.conf": ensure => file, content => template("nagios/proxy.erb"), owner => "root", group => "root", mode => "0644" } }
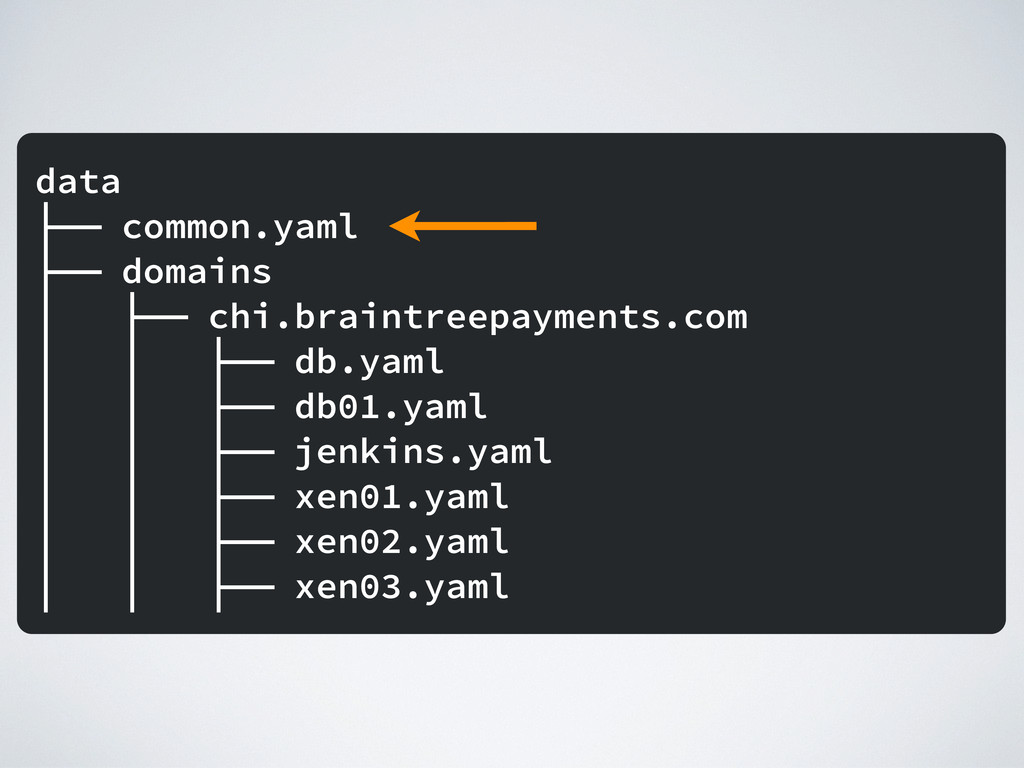
  19. data ├── common.yaml ├── domains │ ├── chi.braintreepayments.com │ │

    ├── db.yaml │ │ ├── db01.yaml │ │ ├── jenkins.yaml │ │ ├── xen01.yaml │ │ ├── xen02.yaml │ │ ├── xen03.yaml
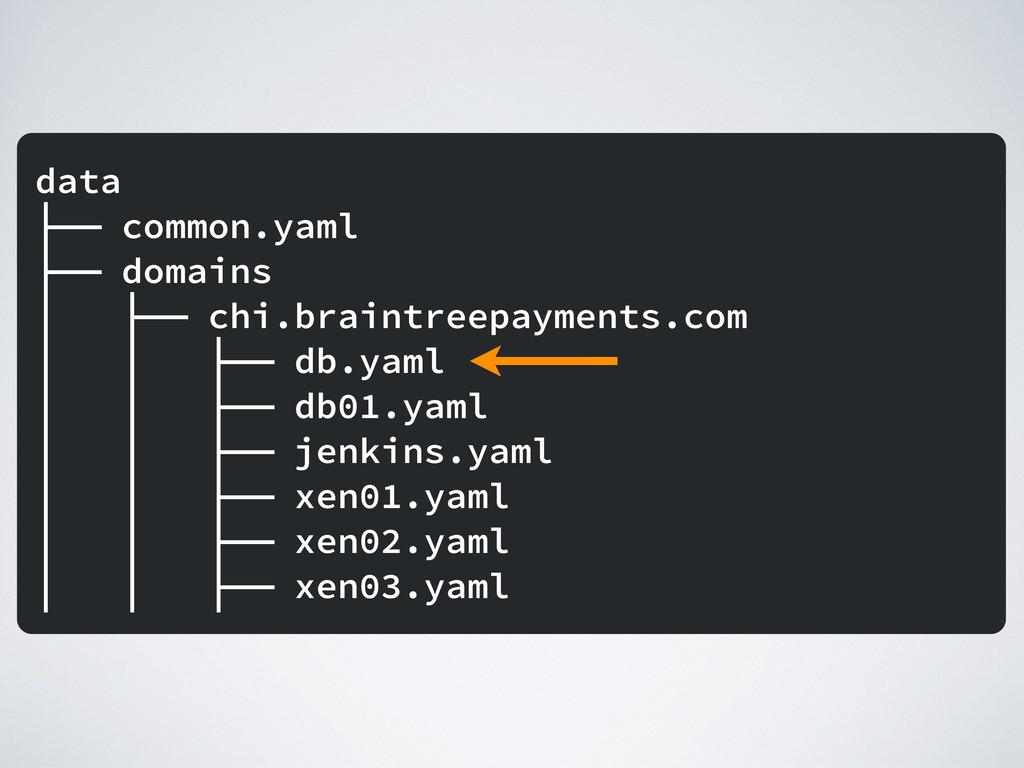
  20. data ├── common.yaml ├── domains │ ├── chi.braintreepayments.com │ │

    ├── db.yaml │ │ ├── db01.yaml │ │ ├── jenkins.yaml │ │ ├── xen01.yaml │ │ ├── xen02.yaml │ │ ├── xen03.yaml
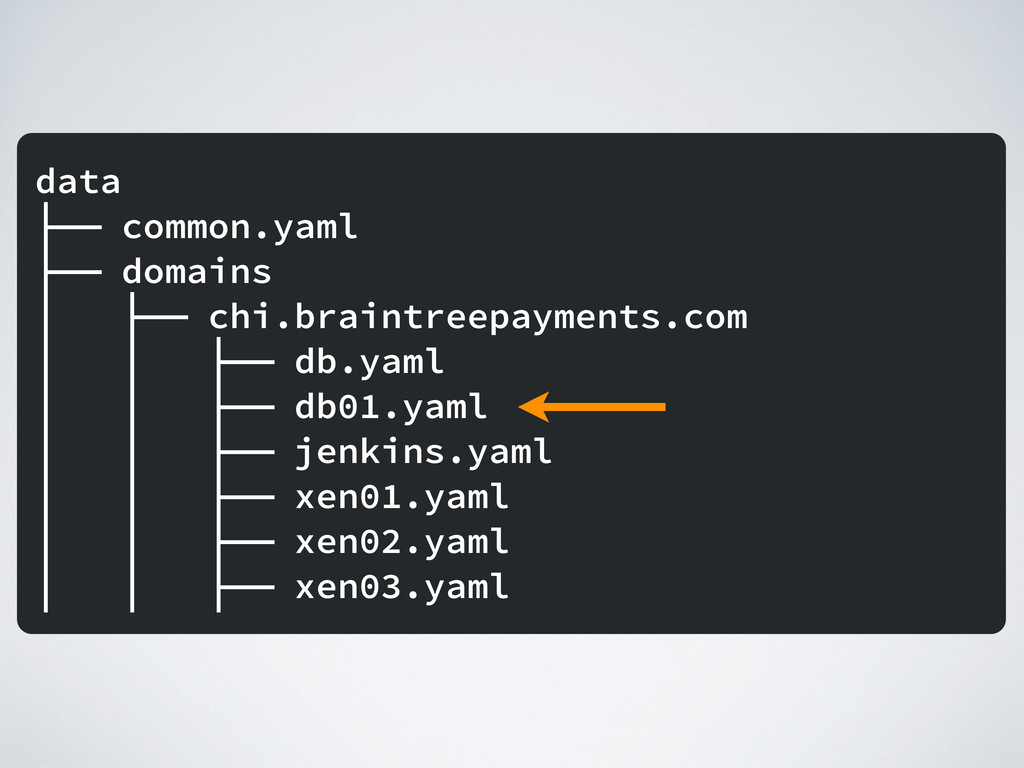
  21. data ├── common.yaml ├── domains │ ├── chi.braintreepayments.com │ │

    ├── db.yaml │ │ ├── db01.yaml │ │ ├── jenkins.yaml │ │ ├── xen01.yaml │ │ ├── xen02.yaml │ │ ├── xen03.yaml
  22. data ├── common.yaml ├── domains │ ├── chi.braintreepayments.com │ │

    ├── db.yaml │ │ ├── db01.yaml │ │ ├── jenkins.yaml │ │ ├── xen01.yaml │ │ ├── xen02.yaml │ │ ├── xen03.yaml
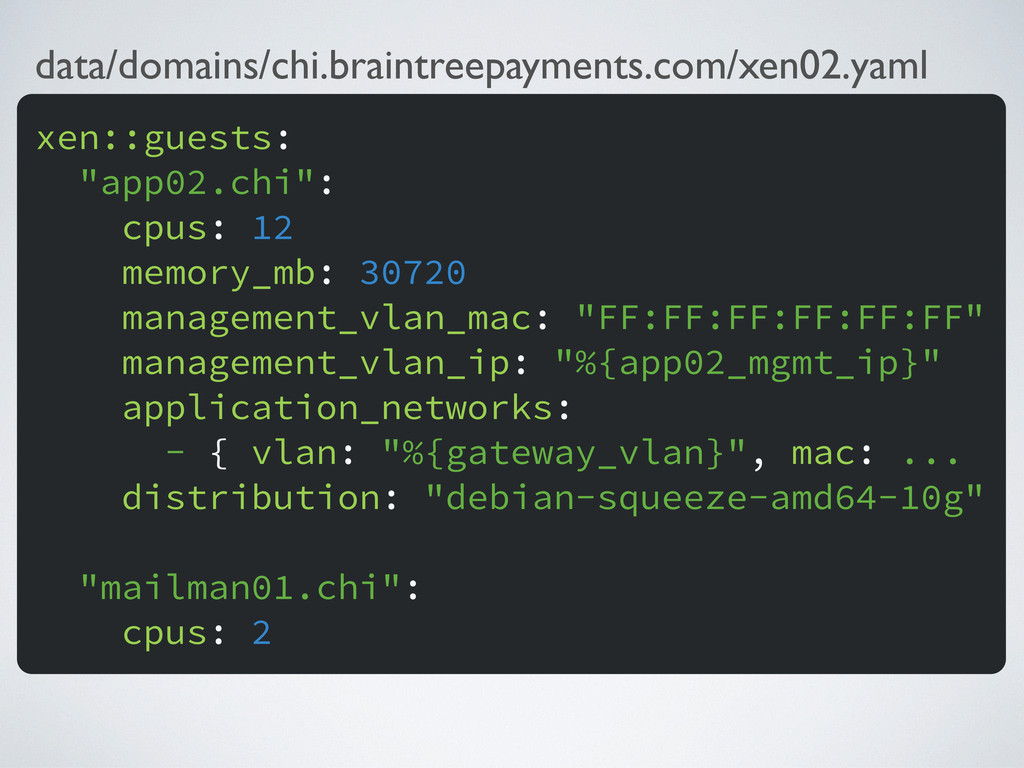
  23. data/domains/chi.braintreepayments.com/xen02.yaml xen::guests: "app02.chi": cpus: 12 memory_mb: 30720 management_vlan_mac: "FF:FF:FF:FF:FF:FF" management_vlan_ip:

    "%{app02_mgmt_ip}" application_networks: - { vlan: "%{gateway_vlan}", mac: ... distribution: "debian-squeeze-amd64-10g" "mailman01.chi": cpus: 2
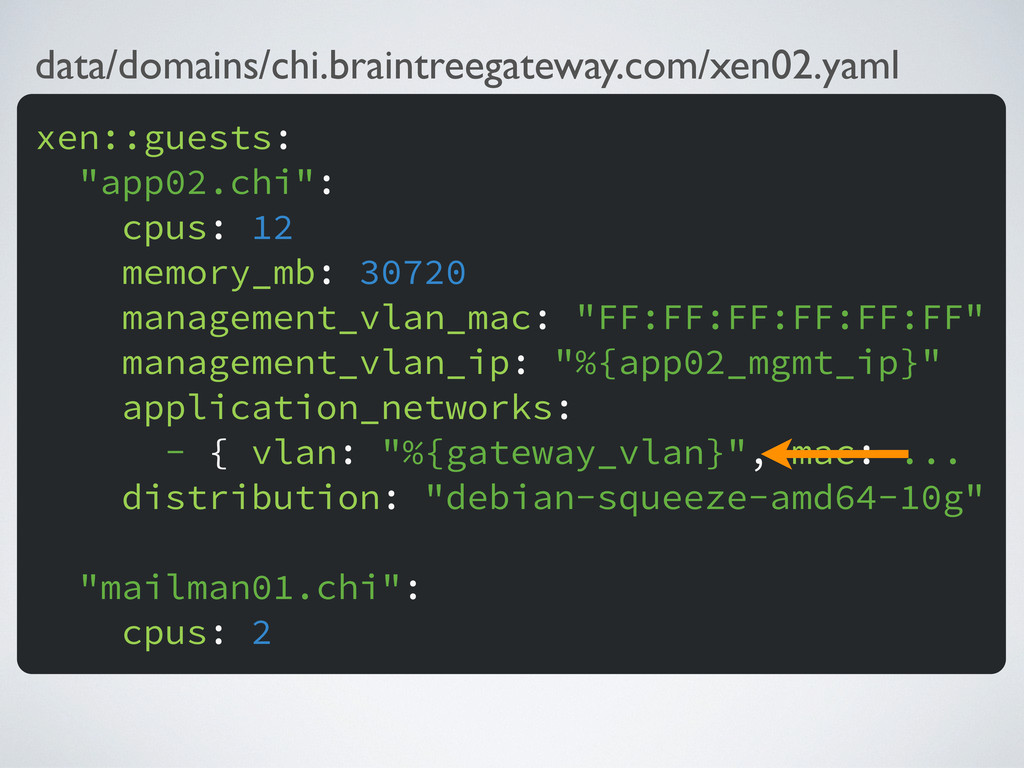
  24. data/domains/chi.braintreegateway.com/xen02.yaml xen::guests: "app02.chi": cpus: 12 memory_mb: 30720 management_vlan_mac: "FF:FF:FF:FF:FF:FF" management_vlan_ip:

    "%{app02_mgmt_ip}" application_networks: - { vlan: "%{gateway_vlan}", mac: ... distribution: "debian-squeeze-amd64-10g" "mailman01.chi": cpus: 2
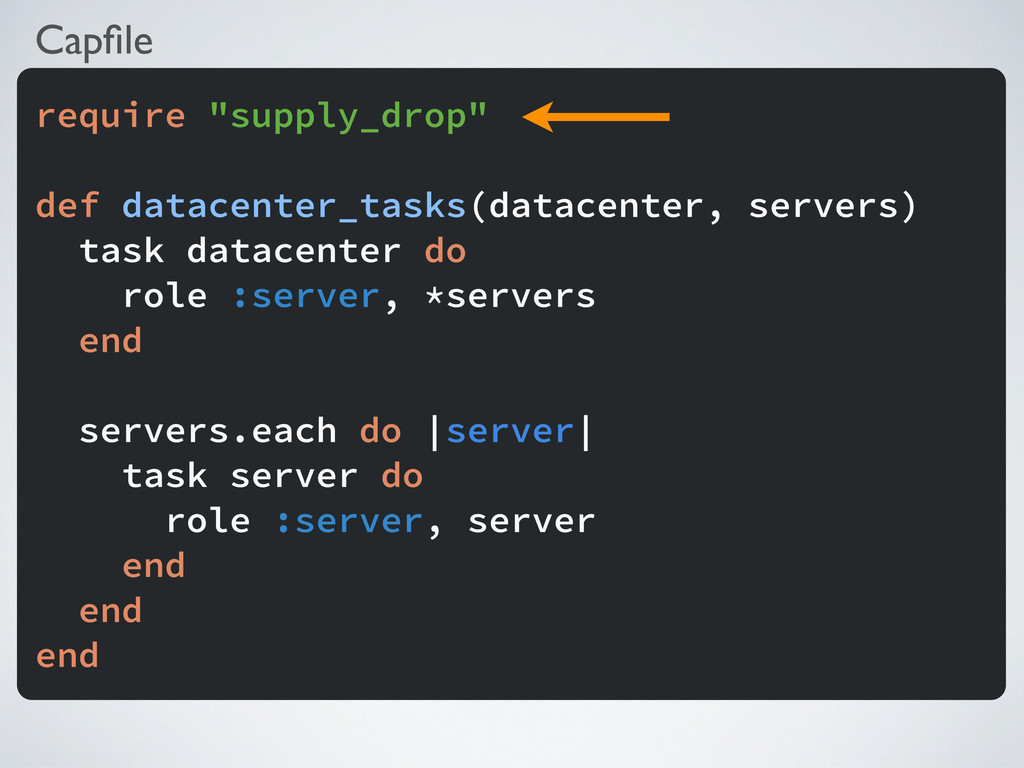
  25. Capfile require "supply_drop" def datacenter_tasks(datacenter, servers) task datacenter do role

    :server, *servers end servers.each do |server| task server do role :server, server end end end
  26. Capfile require "supply_drop" def datacenter_tasks(datacenter, servers) task datacenter do role

    :server, *servers end servers.each do |server| task server do role :server, server end end end
  27. Capfile require "supply_drop" def datacenter_tasks(datacenter, servers) task datacenter do role

    :server, *servers end servers.each do |server| task server do role :server, server end end end
  28. Capfile require "supply_drop" def datacenter_tasks(datacenter, servers) task datacenter do role

    :server, *servers end servers.each do |server| task server do role :server, server end end end
  29. console $ cap app01.qa puppet:noop notice: /Stage[main]/Package[ruby]/ensure: current_value absent, should

    be present (noop) $ cap app01.qa puppet:apply $ cap qa puppet:noop $ git add -Av $ git commit -m "install ruby" $ git push
  30. console $ cap app01.qa puppet:noop notice: /Stage[main]/Package[ruby]/ensure: current_value absent, should

    be present (noop) $ cap app01.qa puppet:apply $ cap qa puppet:noop $ git add -Av $ git commit -m "install ruby" $ git push Always read the diff!!
  31. console $ cap app01.qa puppet:noop notice: /Stage[main]/Package[ruby]/ensure: current_value absent, should

    be present (noop) $ cap app01.qa puppet:apply $ cap qa puppet:noop $ git add -Av $ git commit -m "install ruby" $ git push
  32. console $ cap app01.qa puppet:noop notice: /Stage[main]/Package[ruby]/ensure: current_value absent, should

    be present (noop) $ cap app01.qa puppet:apply $ cap qa puppet:noop $ git add -Av $ git commit -m "install ruby" $ git push
  33. console $ cap app01.qa puppet:noop notice: /Stage[main]/Package[ruby]/ensure: current_value absent, should

    be present (noop) $ cap app01.qa puppet:apply $ cap qa puppet:noop $ git add -Av $ git commit -m "install ruby" $ git push
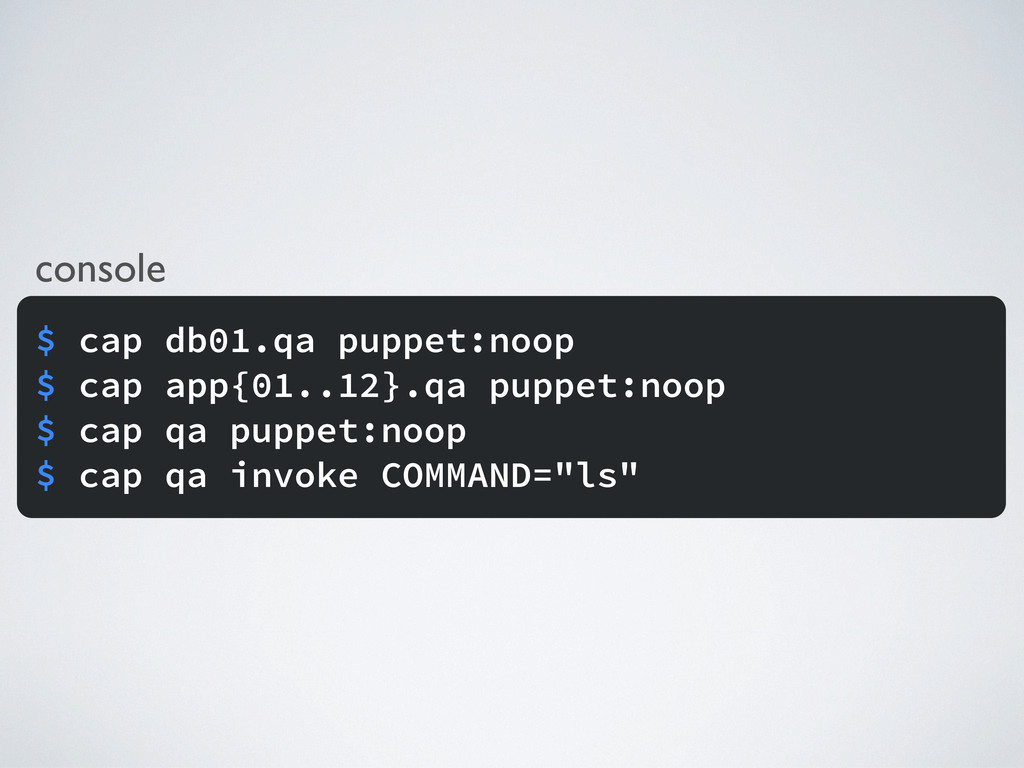
  34. console $ cap db01.qa puppet:noop $ cap app{01..12}.qa puppet:noop $

    cap qa puppet:noop $ cap qa invoke COMMAND="ls"
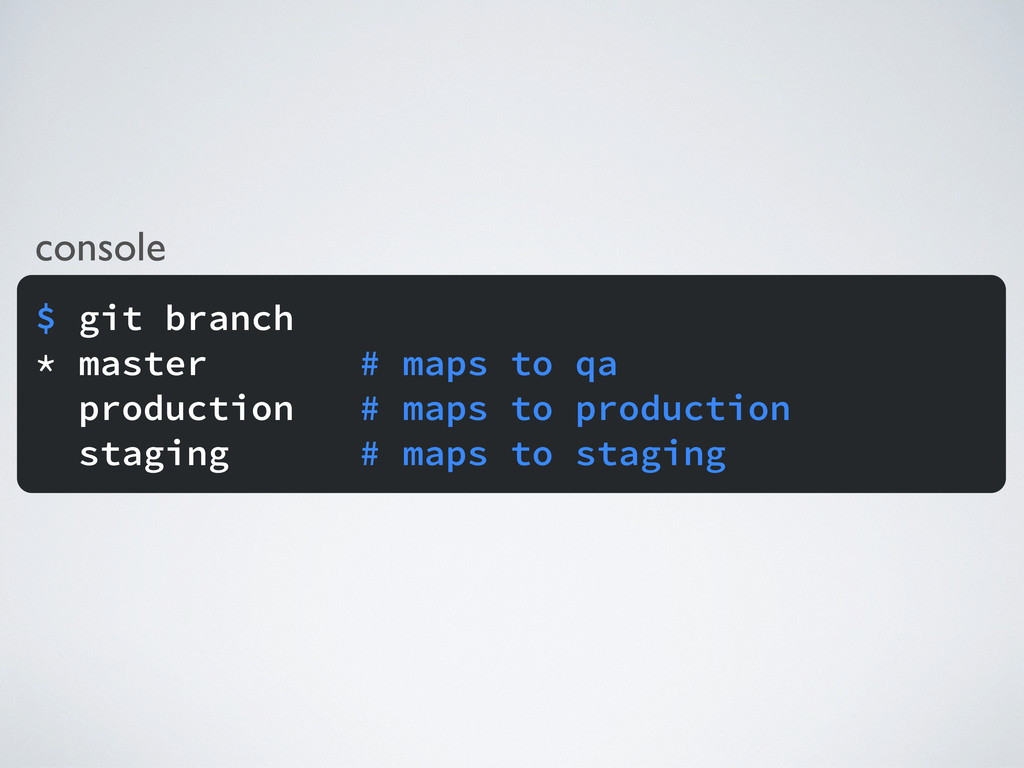
  35. console $ git branch * master # maps to qa

    production # maps to production staging # maps to staging
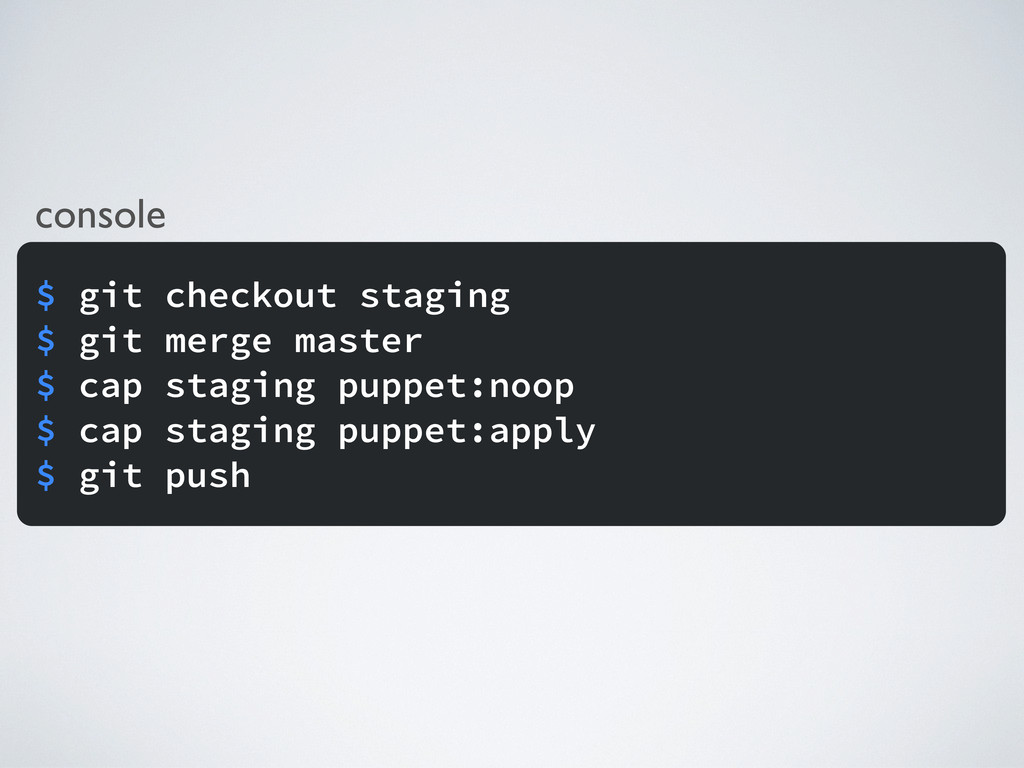
  36. console $ git checkout staging $ git merge master $

    cap staging puppet:noop $ cap staging puppet:apply $ git push
  37. console $ git checkout staging $ git merge master $

    cap staging puppet:noop $ cap staging puppet:apply $ git push
  38. console $ git checkout staging $ git merge master $

    cap staging puppet:noop $ cap staging puppet:apply $ git push
  39. console $ git checkout staging $ git merge master $

    cap staging puppet:noop $ cap staging puppet:apply $ git push
  40. LESSONS LEARNED • Stick to the puppet style guide •

    Use modules • Know where the truth is • Turn on puppet backup file bucket • Merge regularly
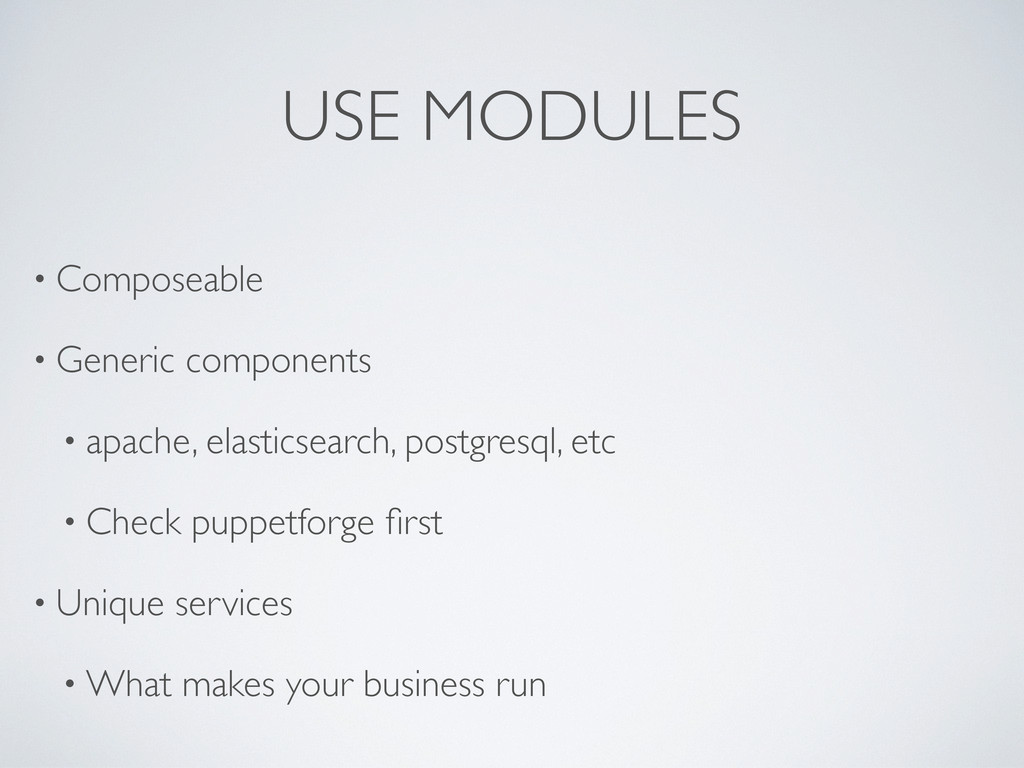
  41. USE MODULES • Composeable • Generic components • apache, elasticsearch,

    postgresql, etc • Check puppetforge first • Unique services • What makes your business run
  42. TRUTH • Use Hiera to manage truth • Don’t let

    it get scattered • Refactor it when you spot it
  43. PUPPET BACKUP • Keep every file version • Great if

    you screw up • Sucks for large files • Turn off per-file
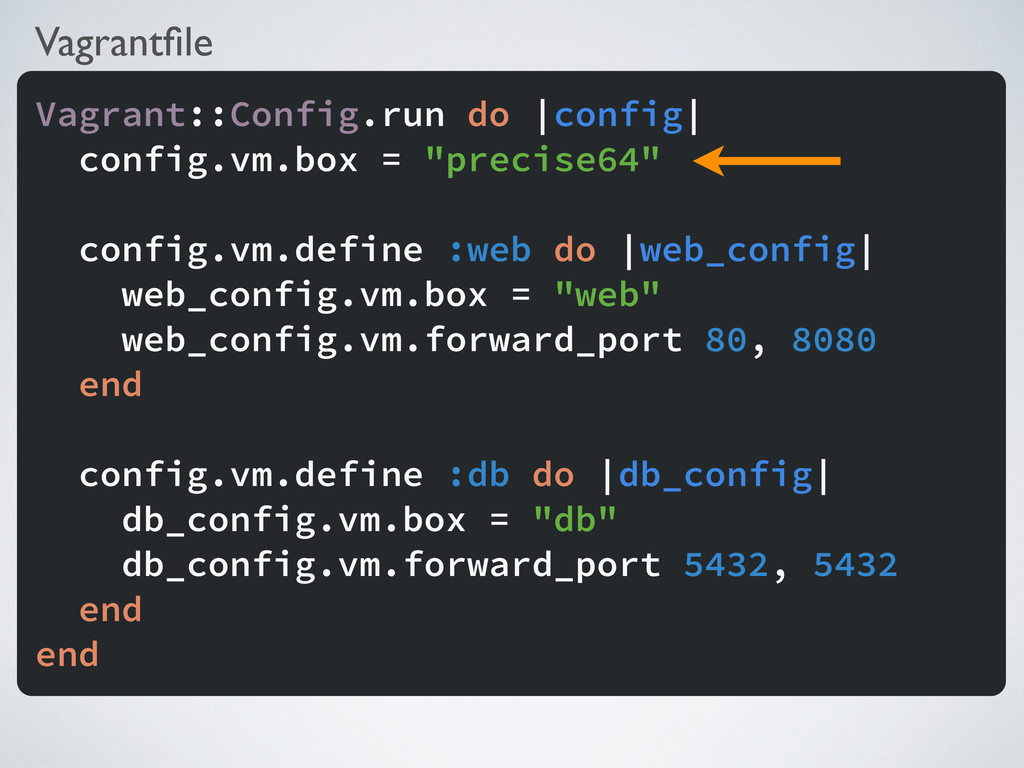
  44. Vagrantfile Vagrant::Config.run do |config| config.vm.box = "precise64" config.vm.define :web do

    |web_config| web_config.vm.box = "web" web_config.vm.forward_port 80, 8080 end config.vm.define :db do |db_config| db_config.vm.box = "db" db_config.vm.forward_port 5432, 5432 end end
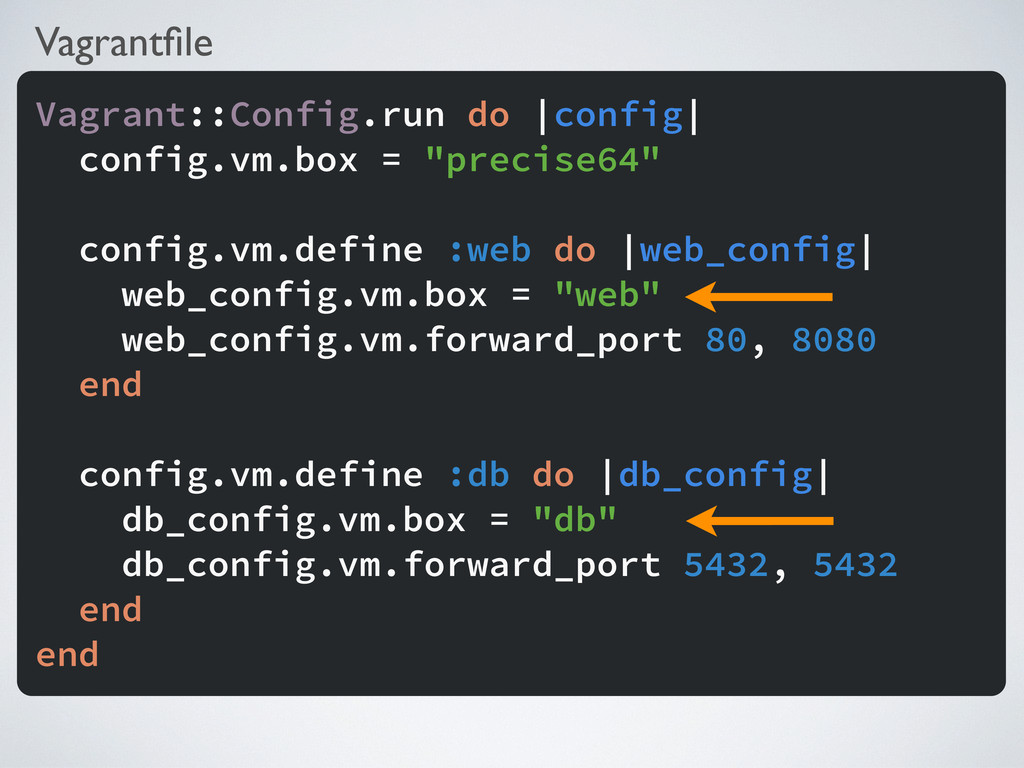
  45. Vagrantfile Vagrant::Config.run do |config| config.vm.box = "precise64" config.vm.define :web do

    |web_config| web_config.vm.box = "web" web_config.vm.forward_port 80, 8080 end config.vm.define :db do |db_config| db_config.vm.box = "db" db_config.vm.forward_port 5432, 5432 end end
  46. Vagrantfile Vagrant::Config.run do |config| config.vm.box = "precise64" config.vm.define :web do

    |web_config| web_config.vm.box = "web" web_config.vm.forward_port 80, 8080 end config.vm.define :db do |db_config| db_config.vm.box = "db" db_config.vm.forward_port 5432, 5432 end end

More Decks by John Downey
Other Decks in Programming