Double Open Automated software compliance 25 years as a tech attorney Built on the open source OSS Review Toolkit Open source advocate: COSS since 2004, steering group since 2009 Hosted or on-premises, wired into CI AI agents triage, people decide doubleopen.io 2
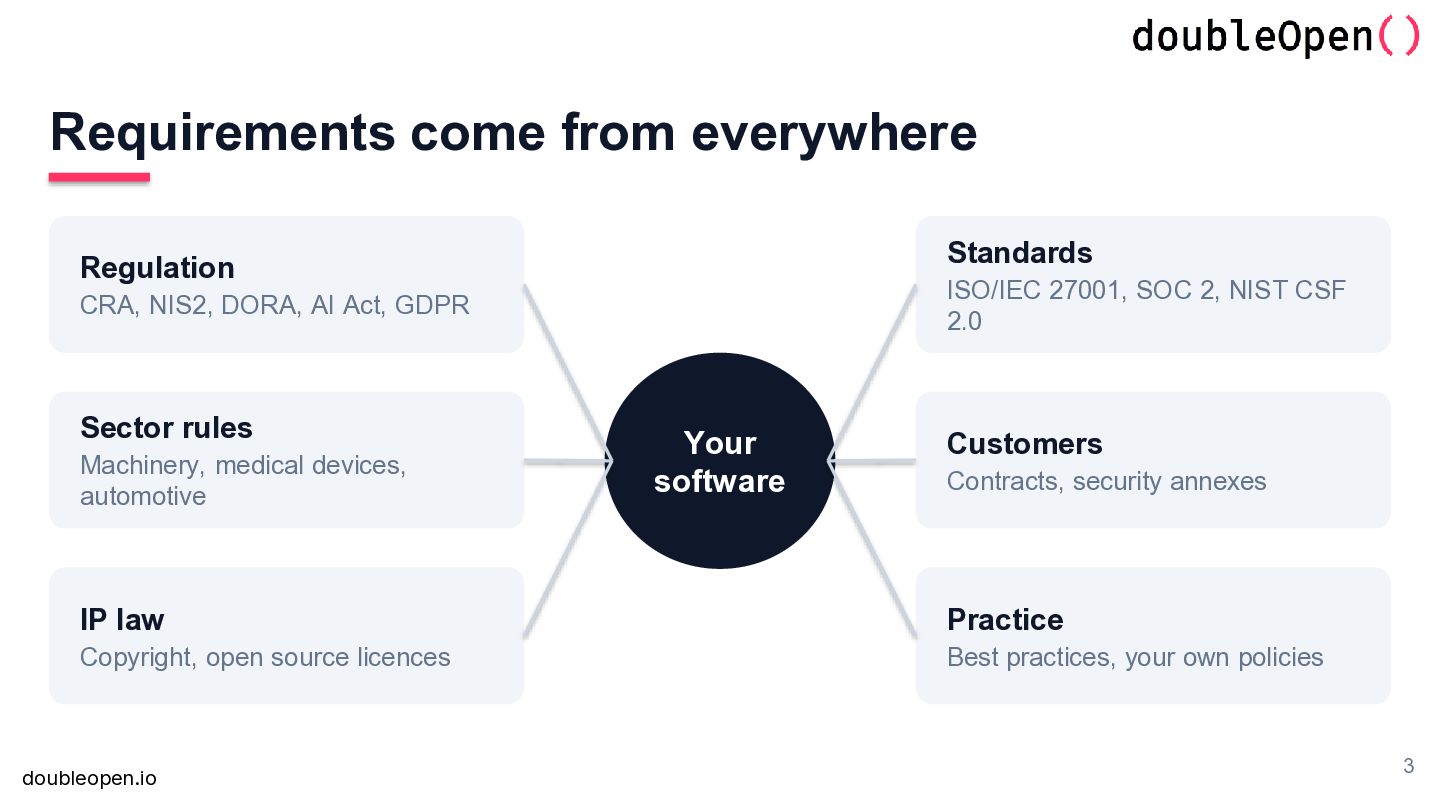
NIST CSF 2.0 CRA, NIS2, DORA, AI Act, GDPR Sector rules Machinery, medical devices, automotive Your software Customers Contracts, security annexes IP law Practice Copyright, open source licences Best practices, your own policies doubleopen.io 3
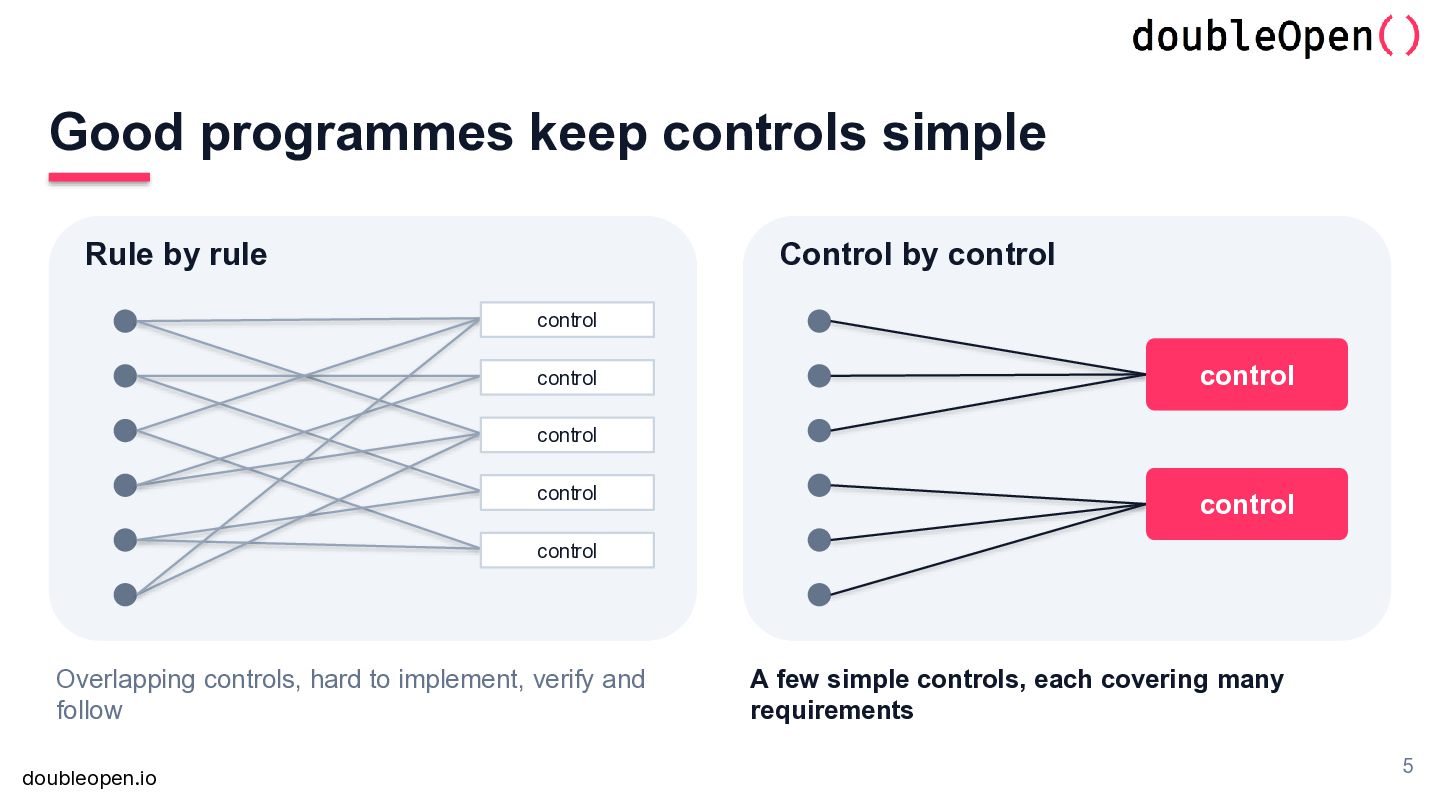
control control control control control control control control Overlapping controls, hard to implement, verify and follow doubleopen.io A few simple controls, each covering many requirements 5
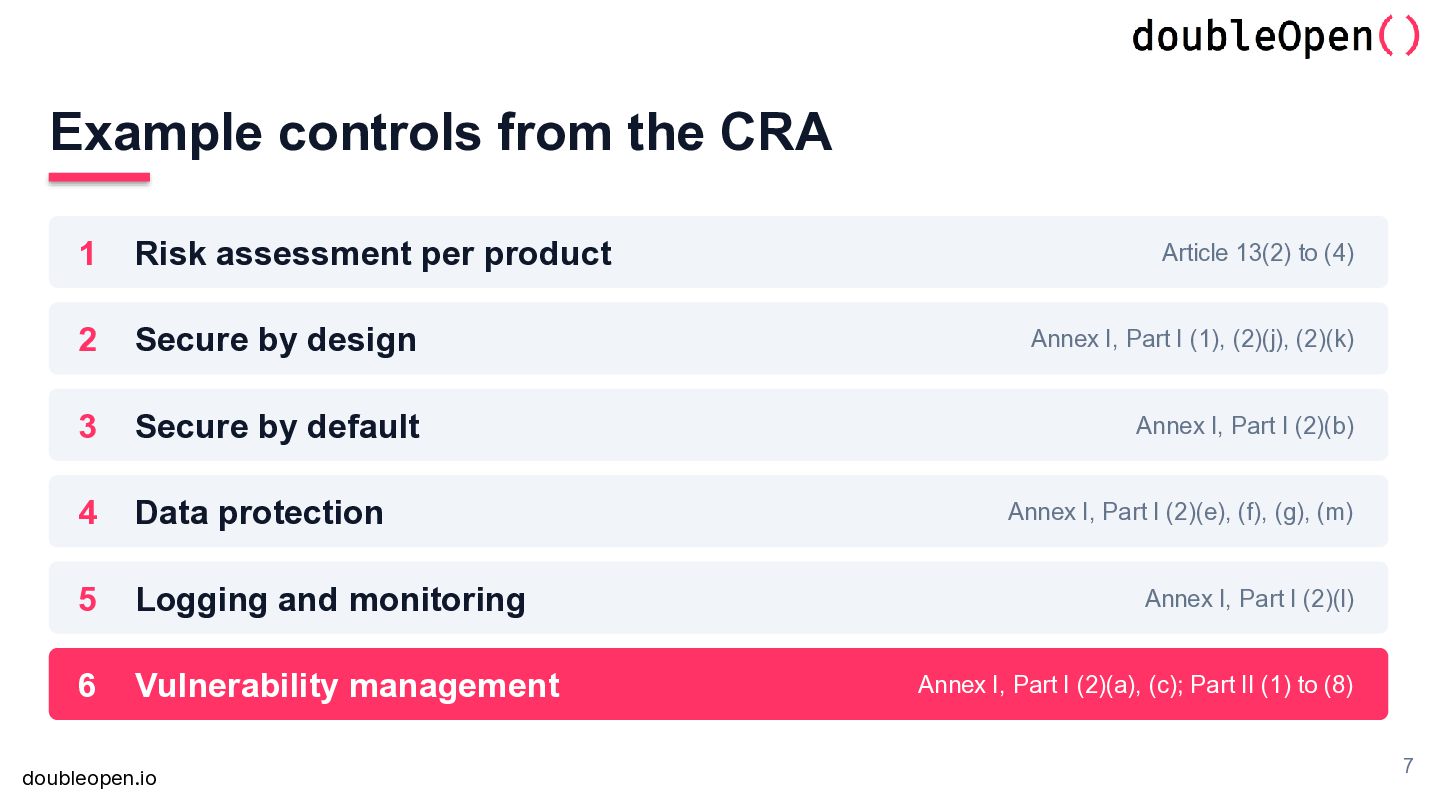
2 Secure by design Annex I, Part I (1), (2)(j), (2)(k) 3 Secure by default Annex I, Part I (2)(b) 4 Data protection 5 Logging and monitoring 6 Vulnerability management doubleopen.io Article 13(2) to (4) Annex I, Part I (2)(e), (f), (g), (m) Annex I, Part I (2)(l) Annex I, Part I (2)(a), (c); Part II (1) to (8) 7
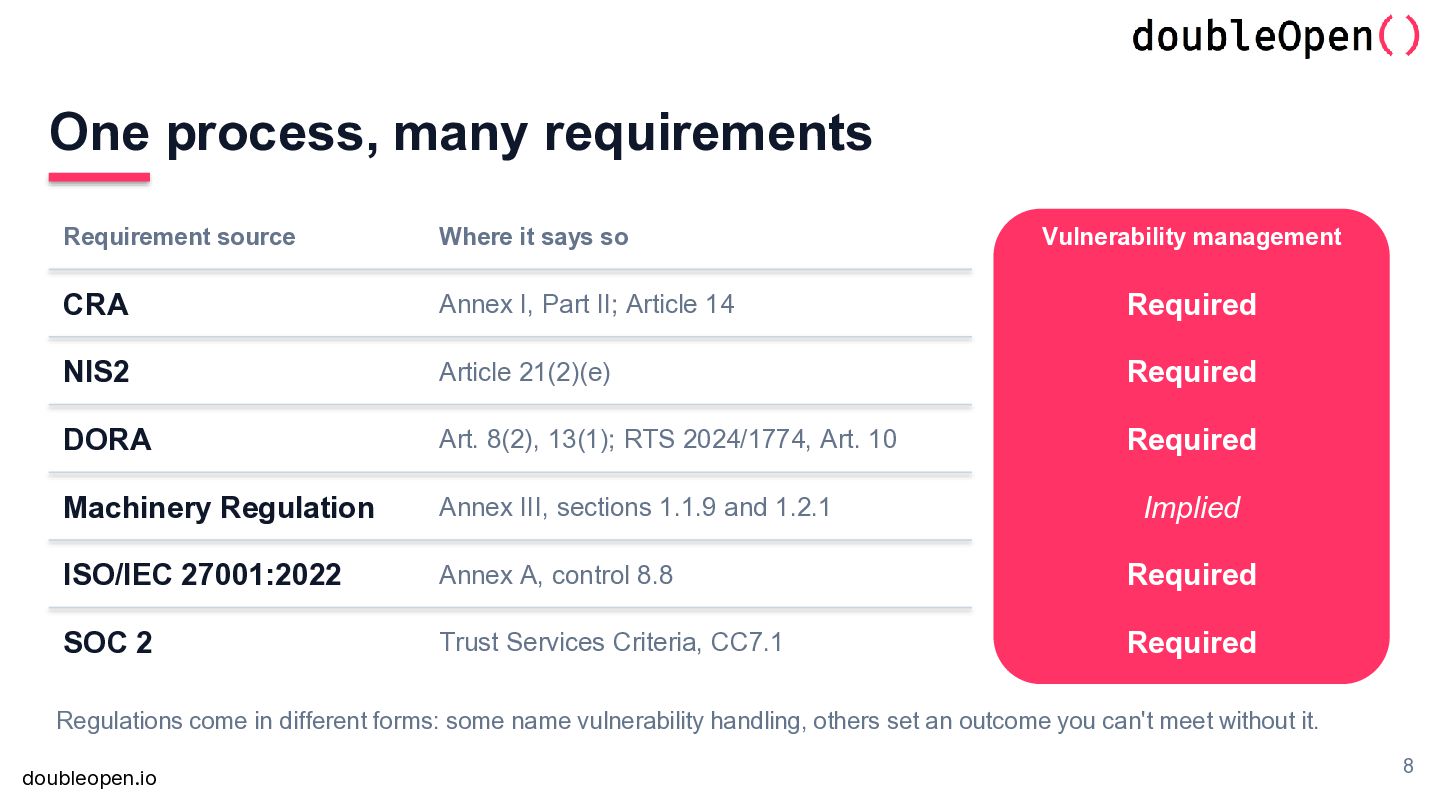
Vulnerability management CRA Annex I, Part II; Article 14 Required NIS2 Article 21(2)(e) Required DORA Art. 8(2), 13(1); RTS 2024/1774, Art. 10 Required Machinery Regulation Annex III, sections 1.1.9 and 1.2.1 Implied ISO/IEC 27001:2022 Annex A, control 8.8 Required SOC 2 Trust Services Criteria, CC7.1 Required Regulations come in different forms: some name vulnerability handling, others set an outcome you can't meet without it. doubleopen.io 8
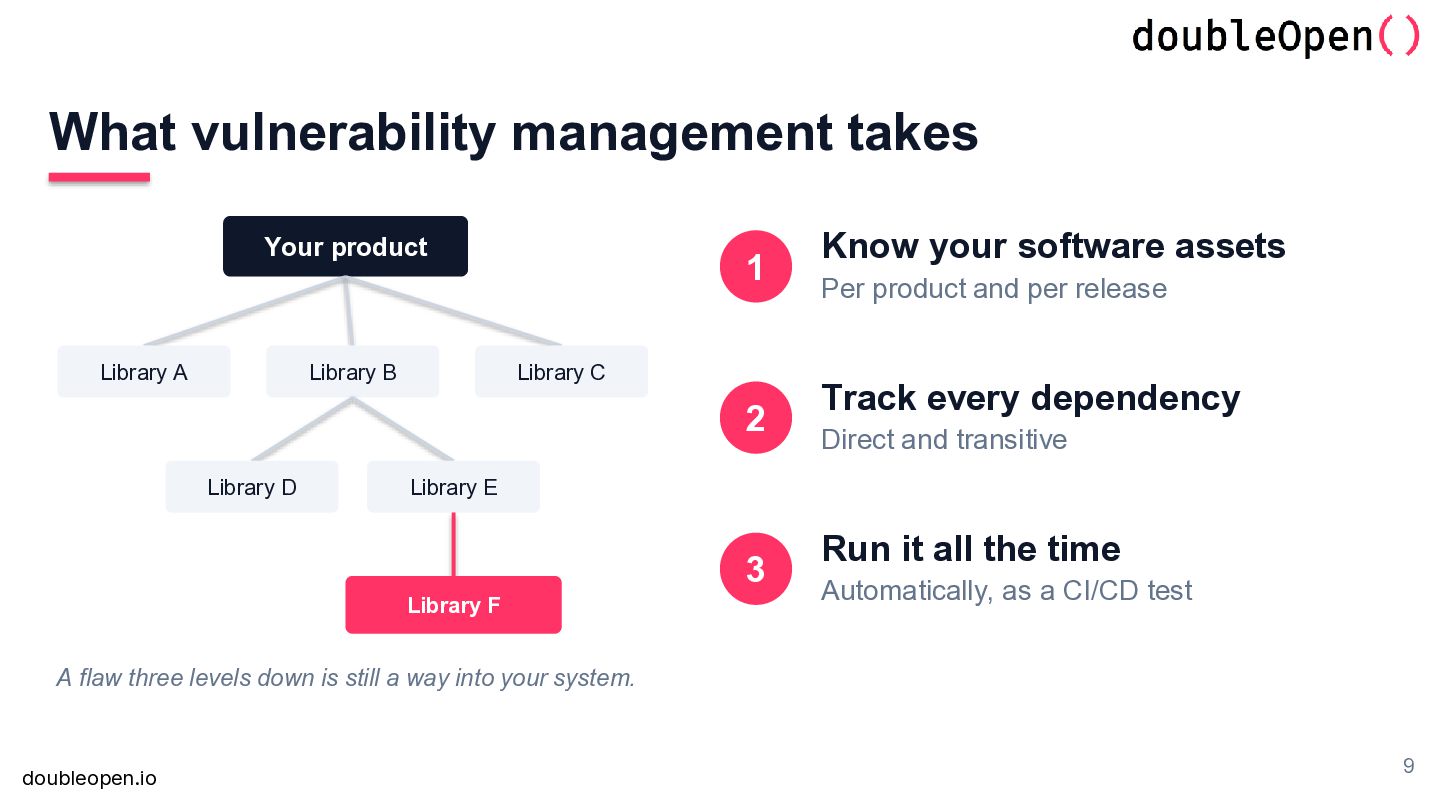
1 Library C 2 Library D Know your software assets Per product and per release Track every dependency Direct and transitive Library E 3 Library F Run it all the time Automatically, as a CI/CD test A flaw three levels down is still a way into your system. doubleopen.io 9
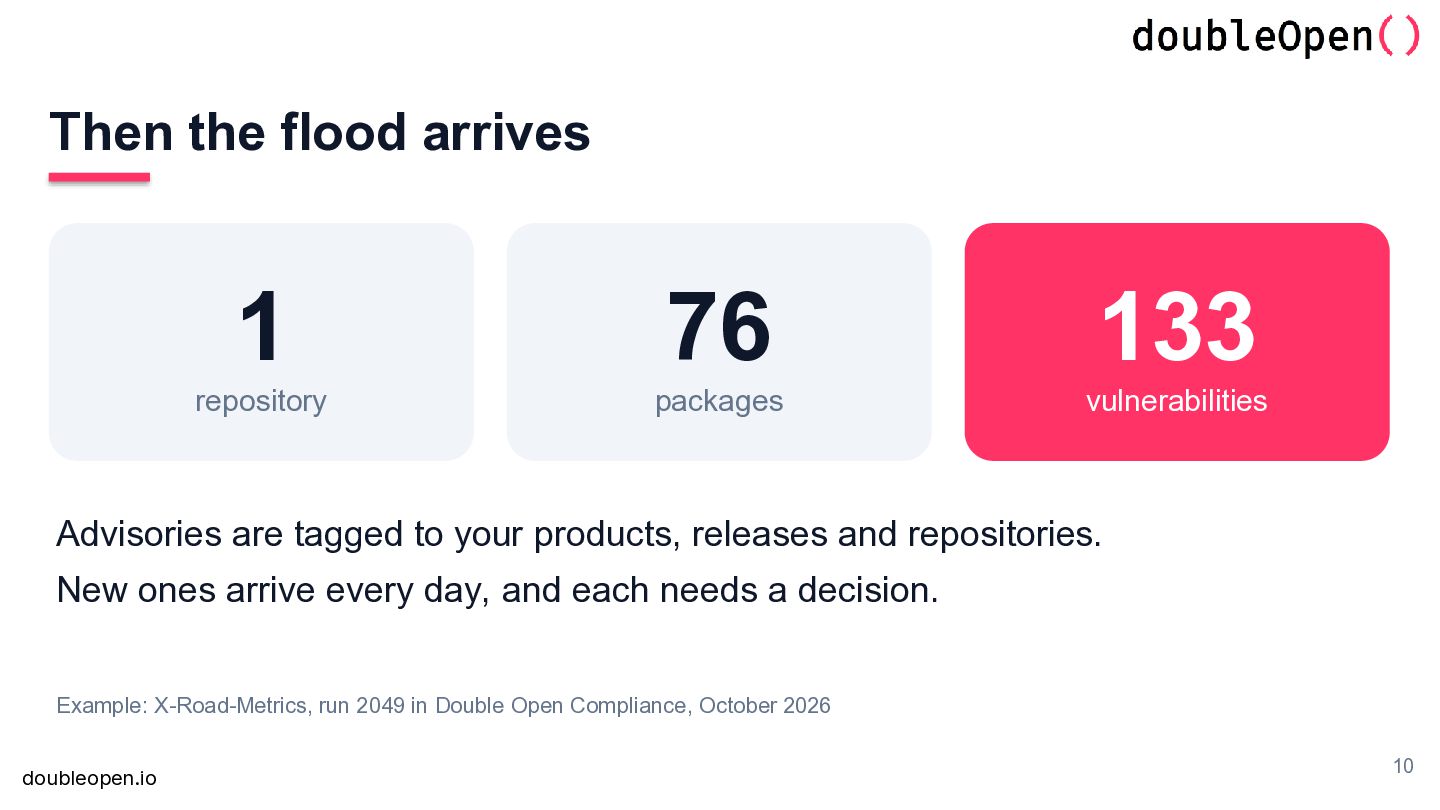
Advisories are tagged to your products, releases and repositories. New ones arrive every day, and each needs a decision. Example: X-Road-Metrics, run 2049 in Double Open Compliance, October 2026 doubleopen.io 10
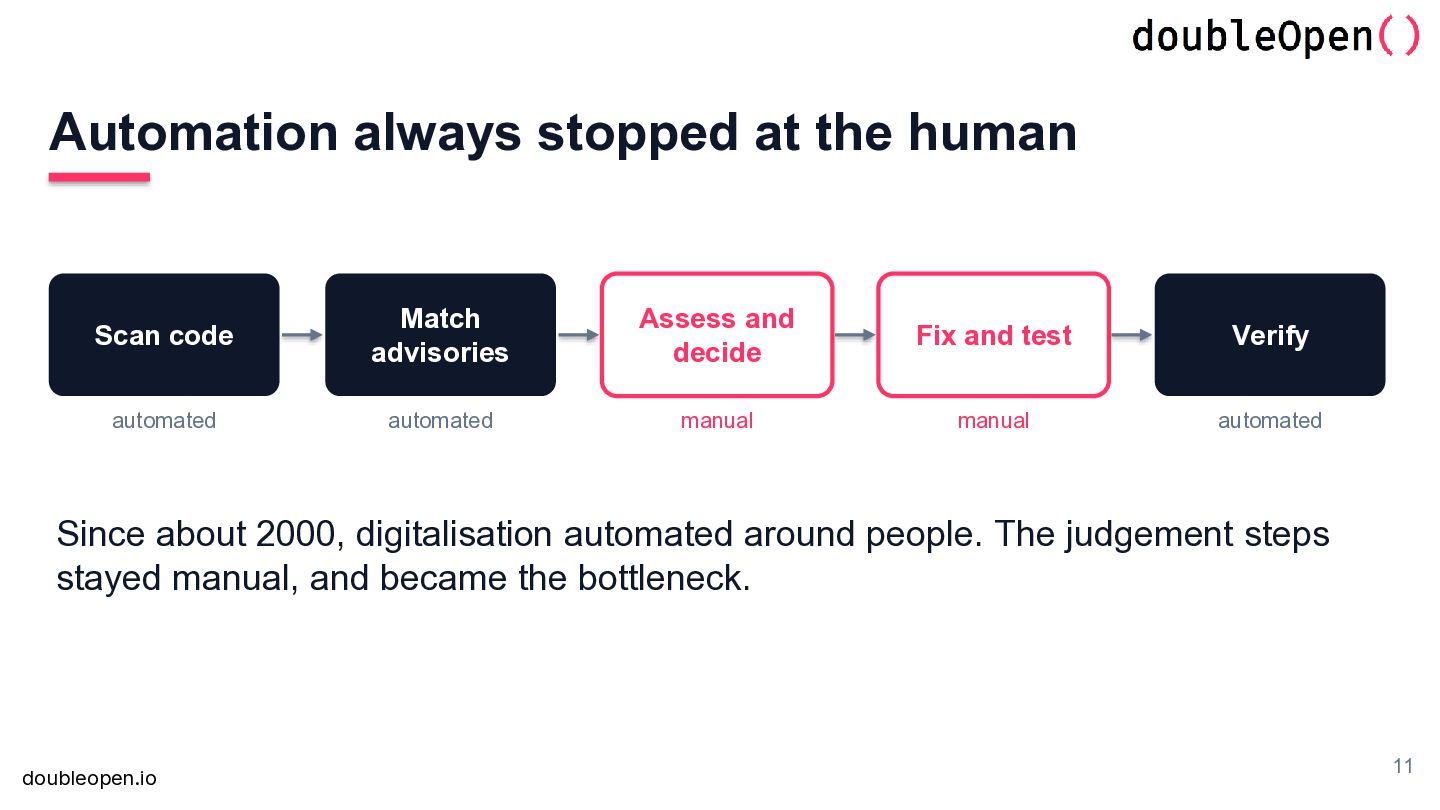
Assess and decide Fix and test Verify automated automated manual manual automated Since about 2000, digitalisation automated around people. The judgement steps stayed manual, and became the bottleneck. doubleopen.io 11
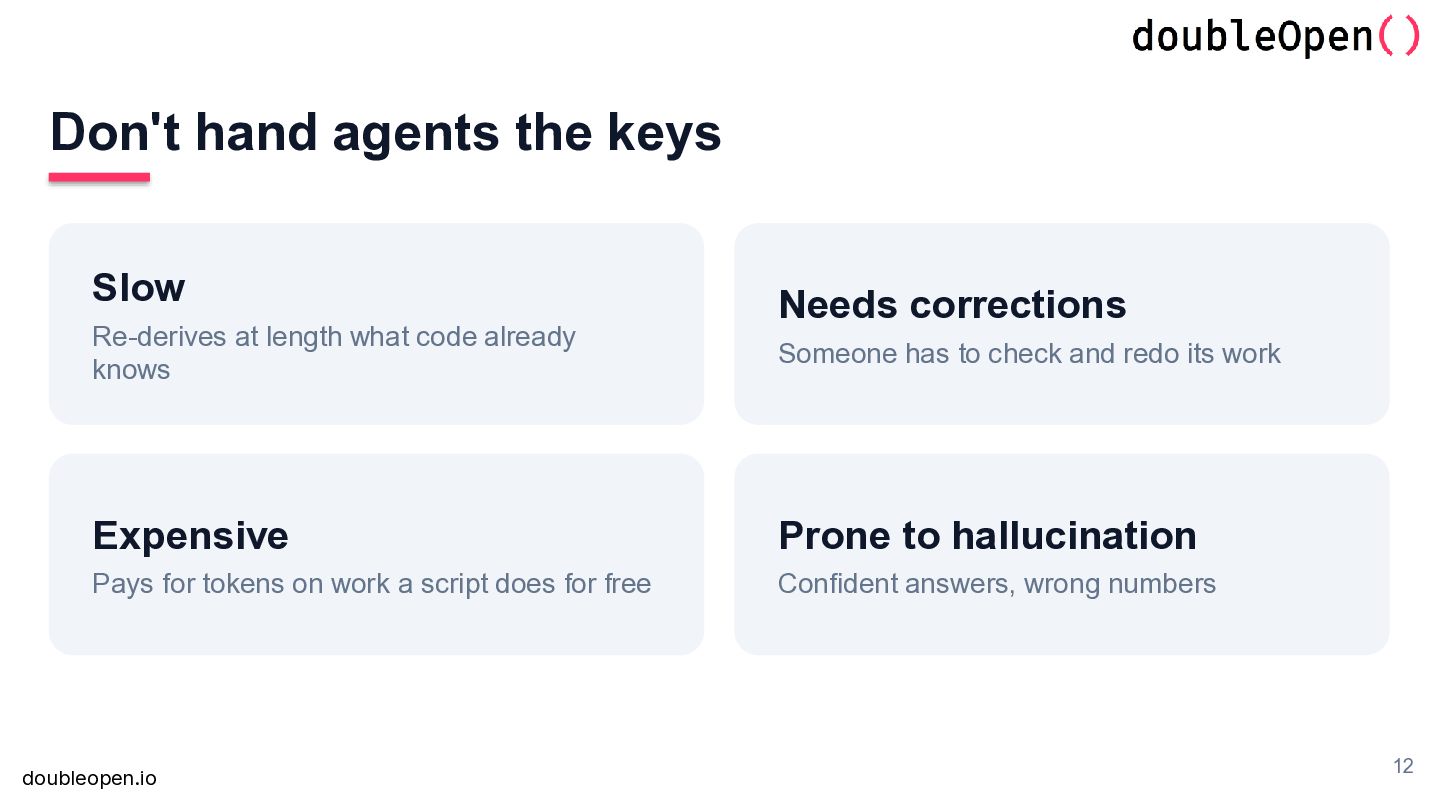
code already knows Needs corrections Someone has to check and redo its work Expensive Prone to hallucination Pays for tokens on work a script does for free Confident answers, wrong numbers doubleopen.io 12
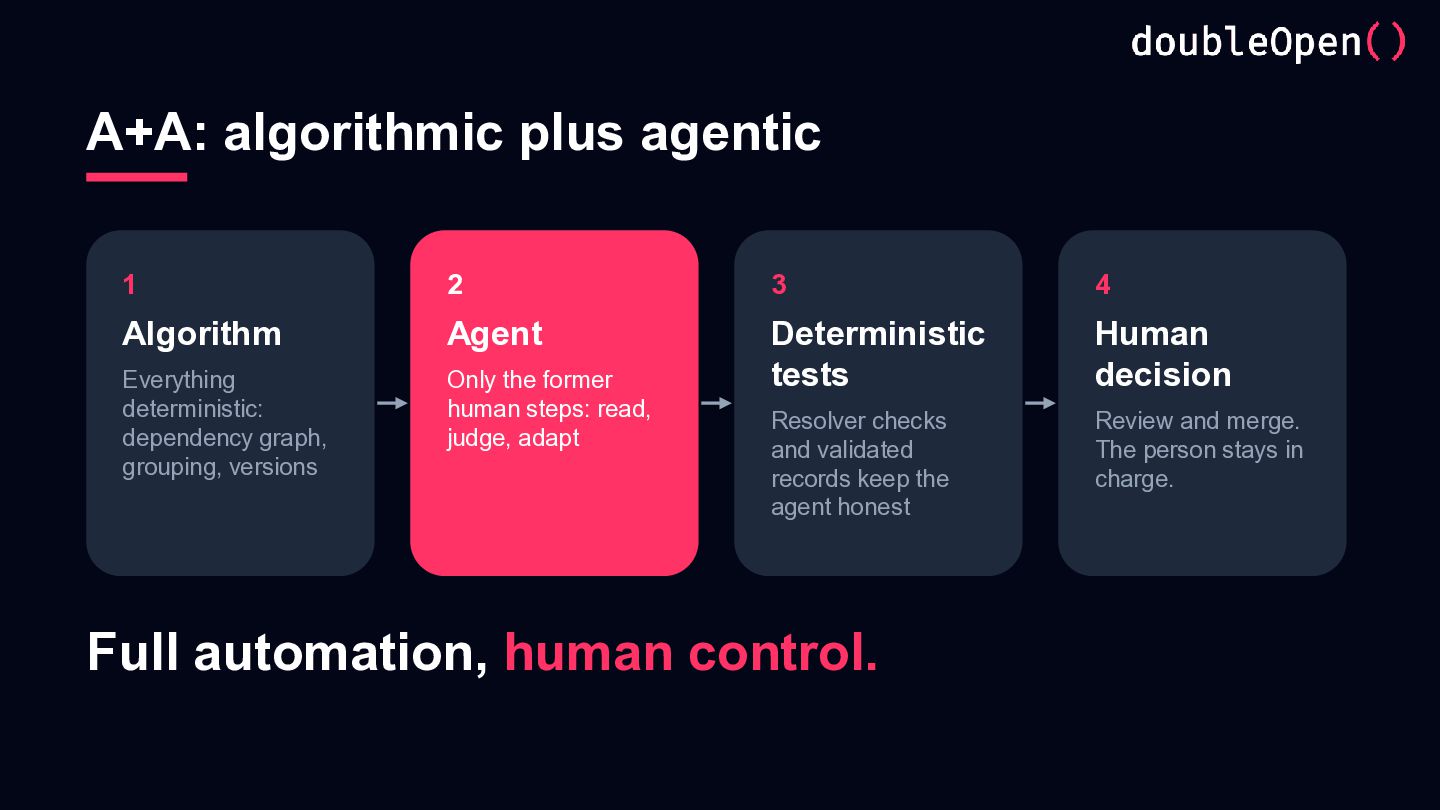
Everything deterministic: dependency graph, grouping, versions Only the former human steps: read, judge, adapt Deterministic tests Human decision Resolver checks and validated records keep the agent honest Review and merge. The person stays in charge. Full automation, human control.
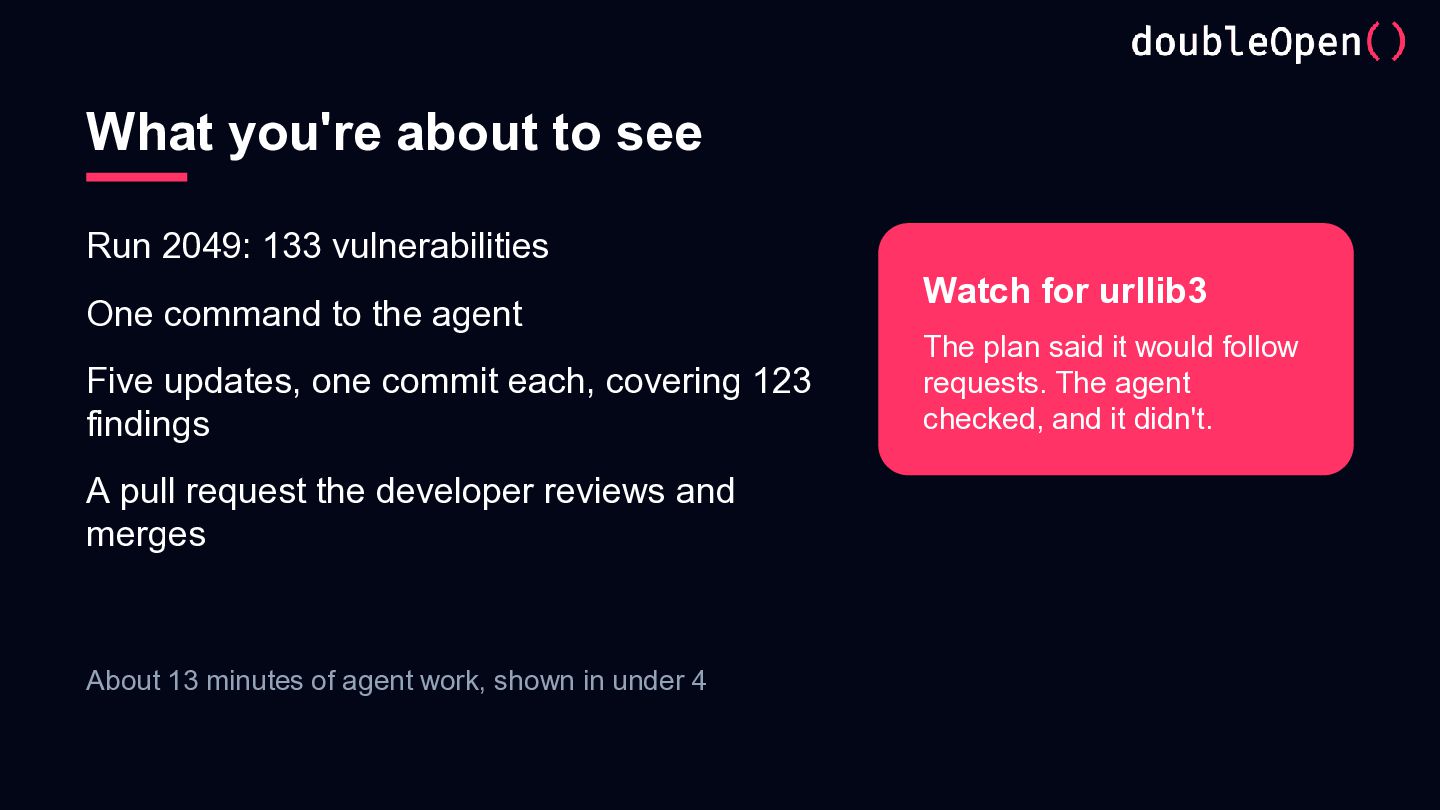
command to the agent Five updates, one commit each, covering 123 findings A pull request the developer reviews and merges About 13 minutes of agent work, shown in under 4 Watch for urllib3 The plan said it would follow requests. The agent checked, and it didn't.
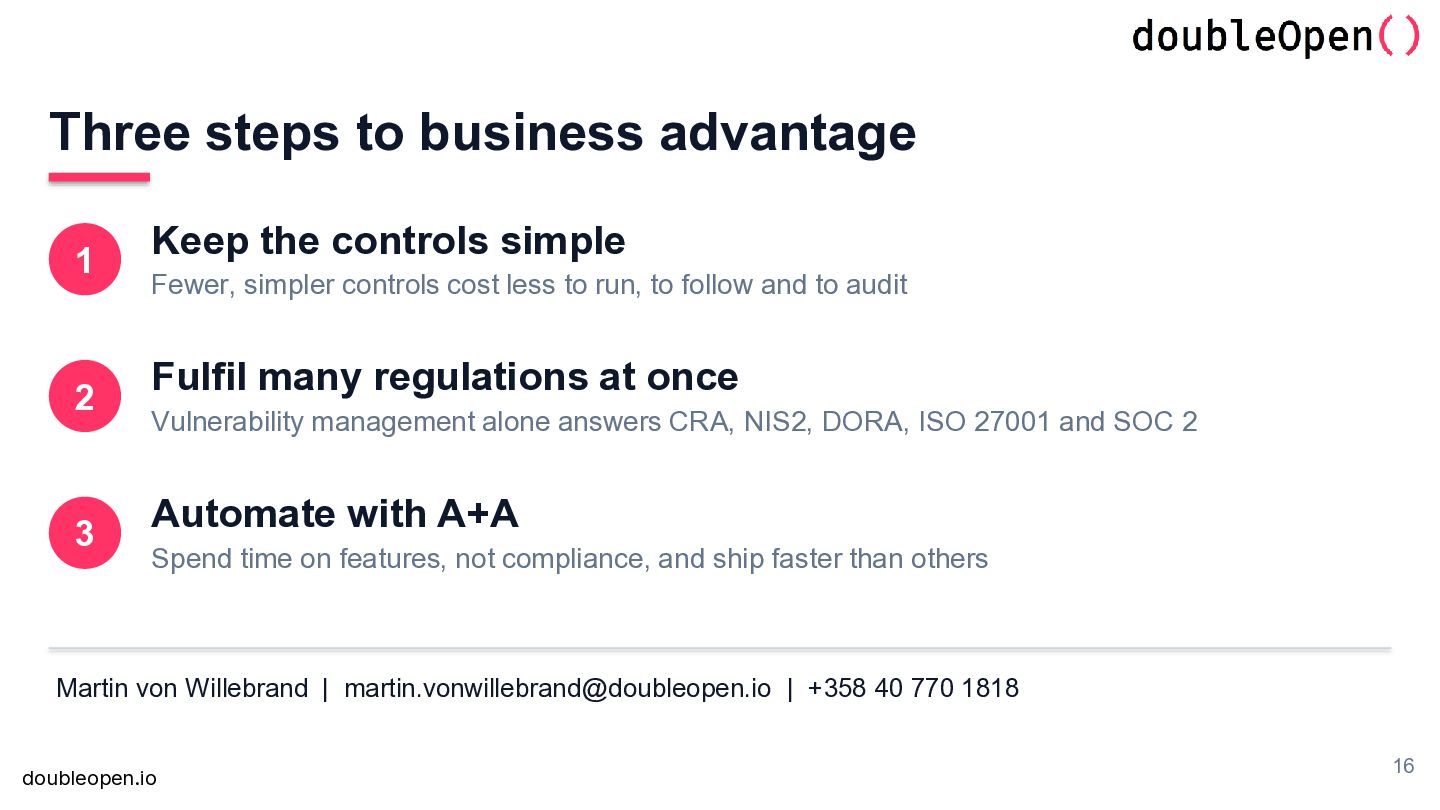
controls simple Fewer, simpler controls cost less to run, to follow and to audit Fulfil many regulations at once Vulnerability management alone answers CRA, NIS2, DORA, ISO 27001 and SOC 2 Automate with A+A Spend time on features, not compliance, and ship faster than others Martin von Willebrand | [email protected] | +358 40 770 1818 doubleopen.io 16


 mindtrekconference
 k1style
 kenichinakamura
 yama3133
 yukiogawa
 kentarofujii
 sansantech
 takahashim
 hamadakoji
 occhi
 tategami
 akizhou
 pfn
 maggiecrowley
 speakerdeck
 khoart
 csswizardry
 kristinabergwall1
 baasie
 eileencodes
 frankvandijk
 greggifford
 nonsquared
 rkendrick25