needs with EU policy, funding and implementation. 1 EU policy engagement Bringing regions’ shared priorities into EU legislation, work programmes and funding frameworks. 2 EU funding Identifying needs-based funding opportunities and coordinating applications and European consortia. 3 Regional and stakeholder cooperation Strengthening cooperation between wellbeing services counties, Helsinki, HUS, national government and European partners.
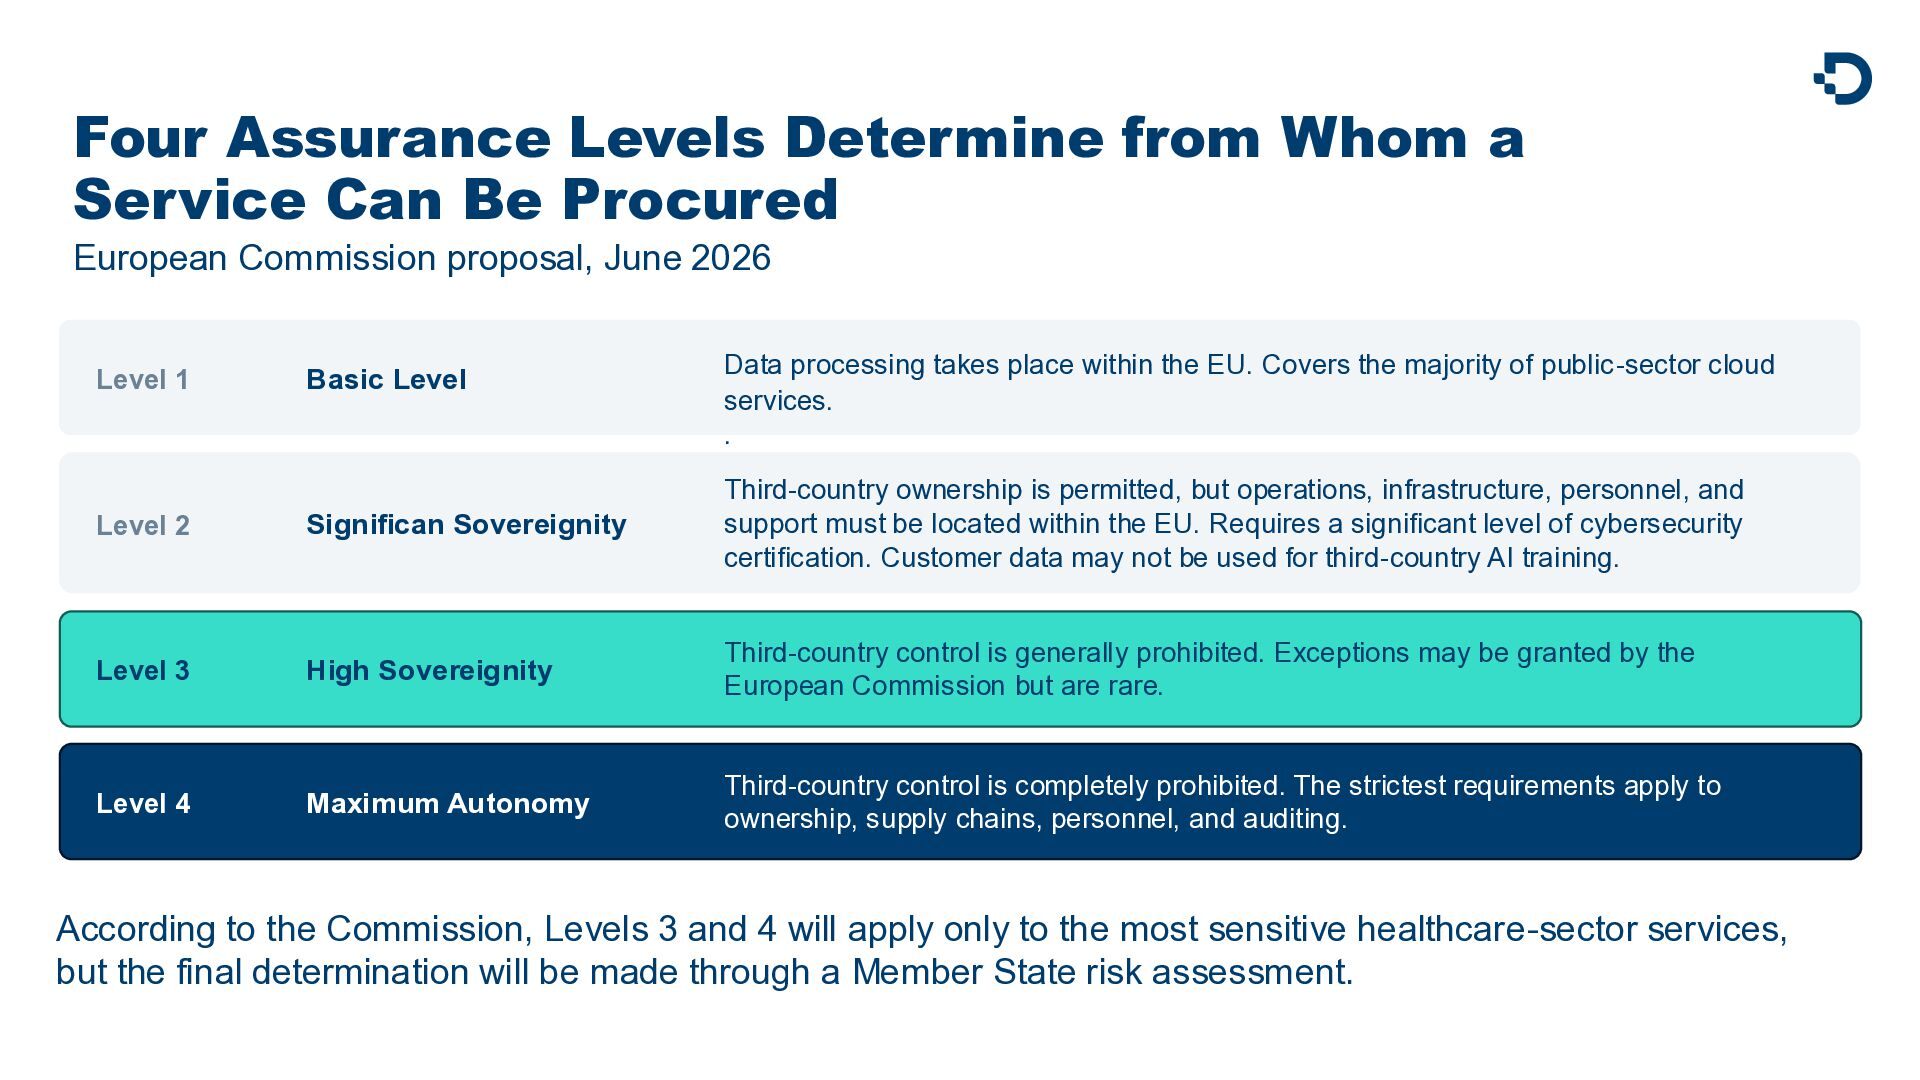
Procured European Commission proposal, June 2026 Level 1 Basic Level Data processing takes place within the EU. Covers the majority of public-sector cloud services. . Level 2 Significan Sovereignity Third-country ownership is permitted, but operations, infrastructure, personnel, and support must be located within the EU. Requires a significant level of cybersecurity certification. Customer data may not be used for third-country AI training. Level 3 High Sovereignity Third-country control is generally prohibited. Exceptions may be granted by the European Commission but are rare. Level 4 Maximum Autonomy Third-country control is completely prohibited. The strictest requirements apply to ownership, supply chains, personnel, and auditing. According to the Commission, Levels 3 and 4 will apply only to the most sensitive healthcare-sector services, but the final determination will be made through a Member State risk assessment.
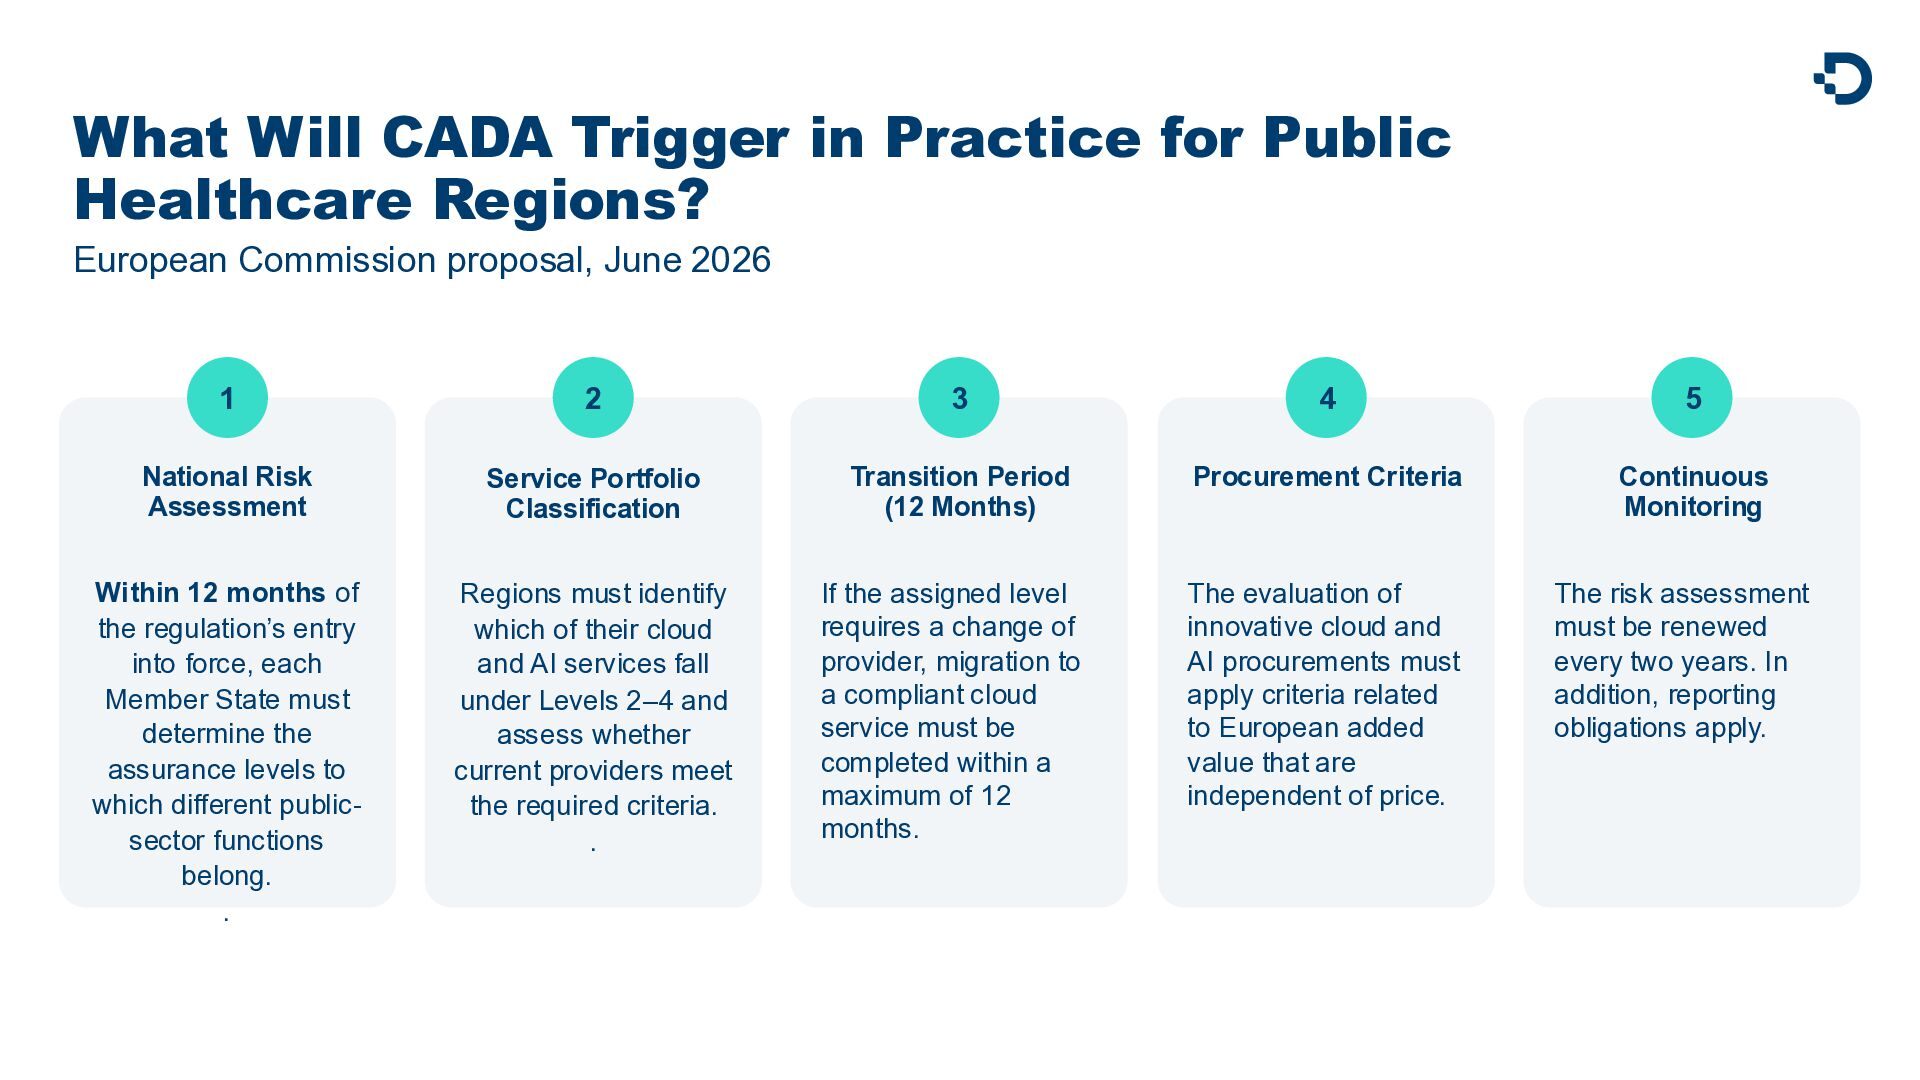
European Commission proposal, June 2026 1 2 3 4 5 National Risk Assessment Service Portfolio Classification Transition Period (12 Months) Procurement Criteria Continuous Monitoring Within 12 months of the regulation’s entry into force, each Member State must determine the assurance levels to which different publicsector functions belong. . Regions must identify which of their cloud and AI services fall under Levels 2–4 and assess whether current providers meet the required criteria. . If the assigned level requires a change of provider, migration to a compliant cloud service must be completed within a maximum of 12 months. The evaluation of innovative cloud and AI procurements must apply criteria related to European added value that are independent of price. The risk assessment must be renewed every two years. In addition, reporting obligations apply.


 mindtrekconference
 kentarofujii
 murachiakira
 watany
 takuroabe
 oasis1994liveforever
 kenichinakamura
 recruitengineers
 usanchuu
 reuven
 gionn
 mhlyc
 emiki
 cassininazir
 skoyamalab
 denniskardys
 konakalab
 jmmastey
 moore
 greggifford
 samtorres
 ianozsvald
 aleyda
 rakko