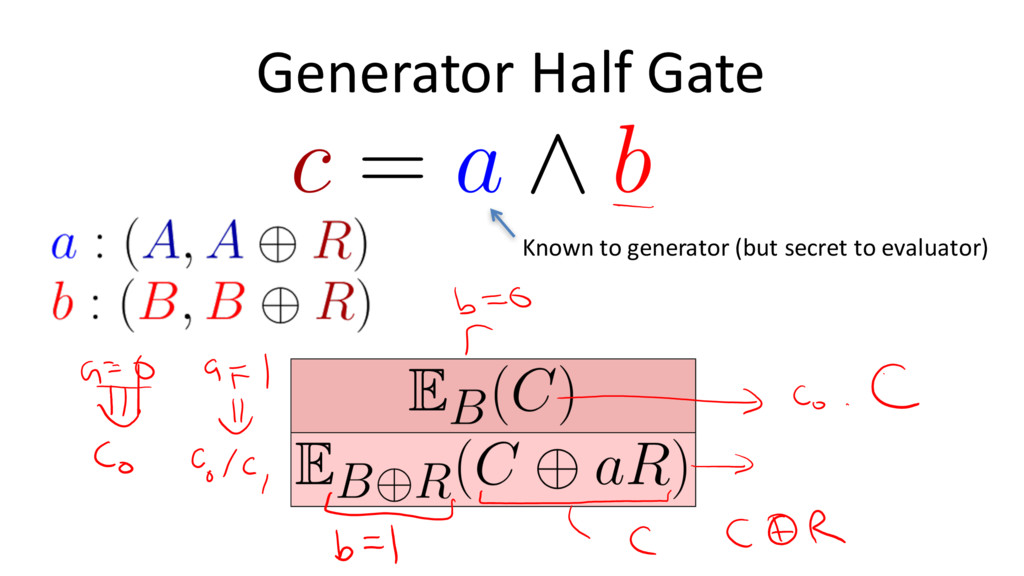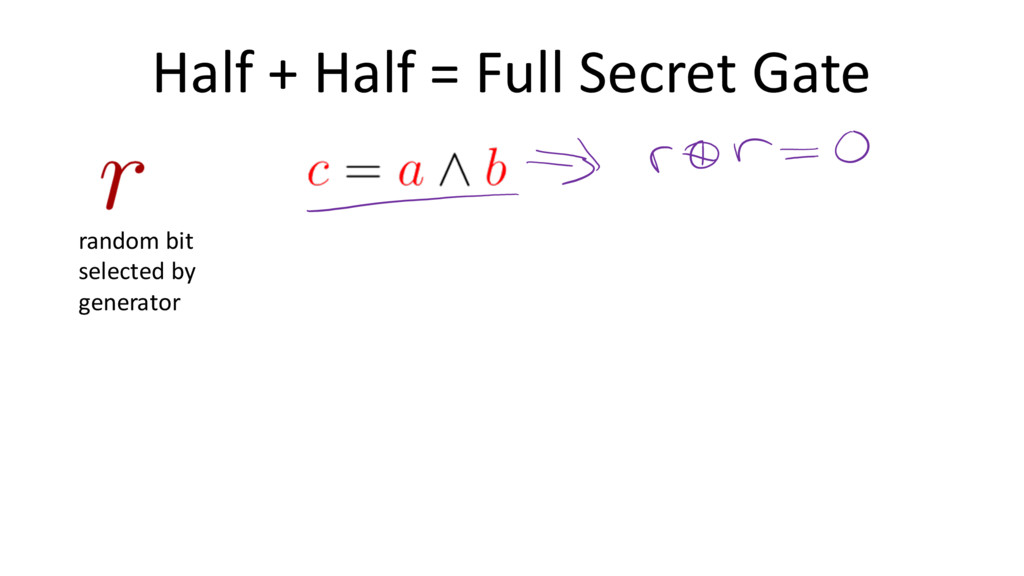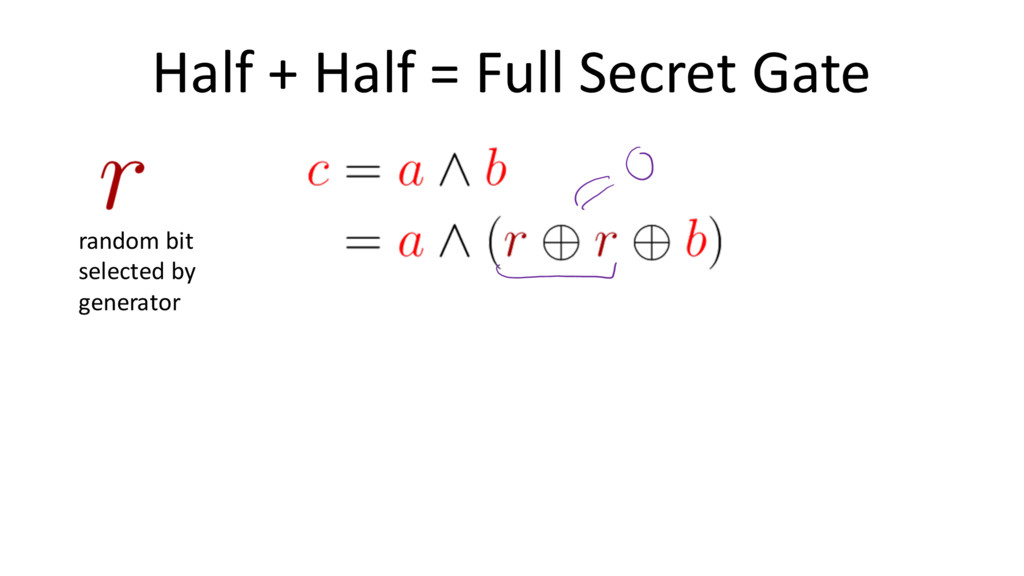Share
Embed
Garbling Techniques
Tutorial at Summer School on Secure and Oblivious Computation and Outsourcing
Notre Dame University, 9 May 2016
David Evans
May 09, 2016
Transcript
71 slides
-
Garbling Techniques David Evans www.cs.virginia.edu/evans Summer School on Secure Computation
University of Notre Dame 9 May 2016 -
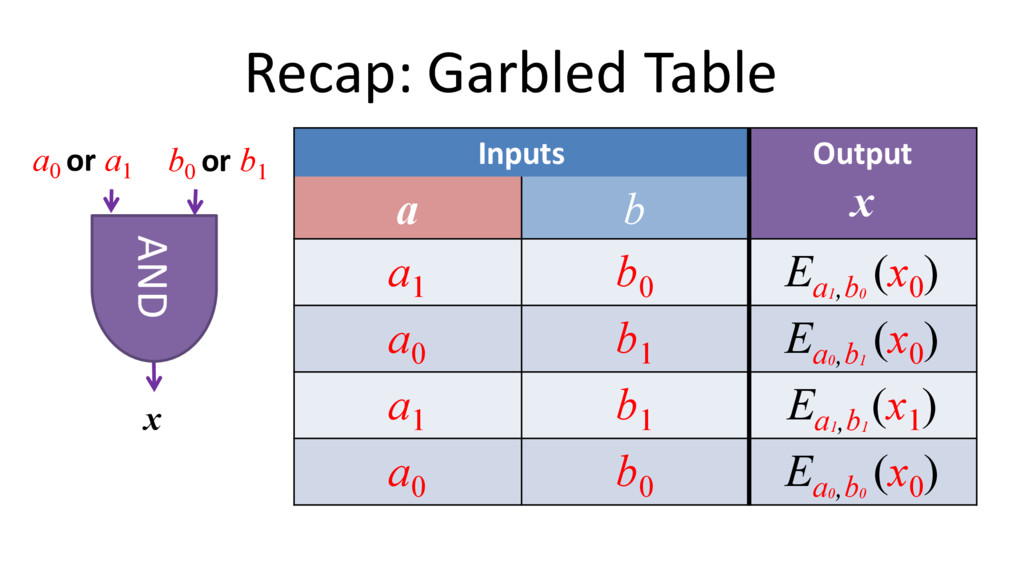
Recap: Garbled Table Inputs Output x a b a1 b0
Ea1 ,b0 (x0 ) a0 b1 Ea0 ,b1 (x0 ) a1 b1 Ea1 ,b1 (x1 ) a0 b0 Ea0 ,b0 (x0 ) a0 or a1 x AND b0 or b1 -
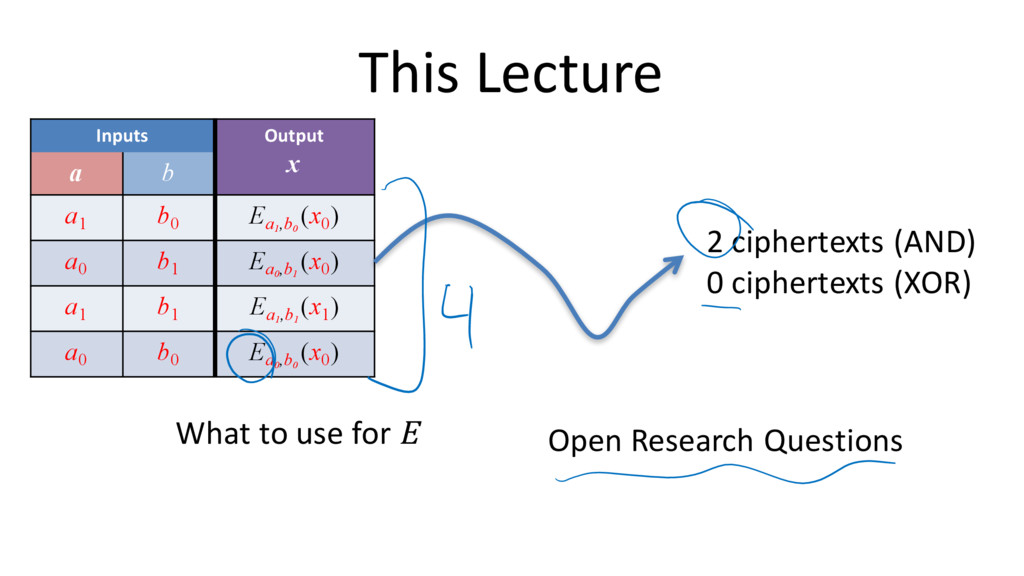
This Lecture Inputs Output x a b a1 b0 Ea1
,b0 (x0 ) a0 b1 Ea0 ,b1 (x0 ) a1 b1 Ea1 ,b1 (x1 ) a0 b0 Ea0 ,b0 (x0 ) 2 ciphertexts (AND) 0 ciphertexts (XOR) What to use for E Open Research Questions -
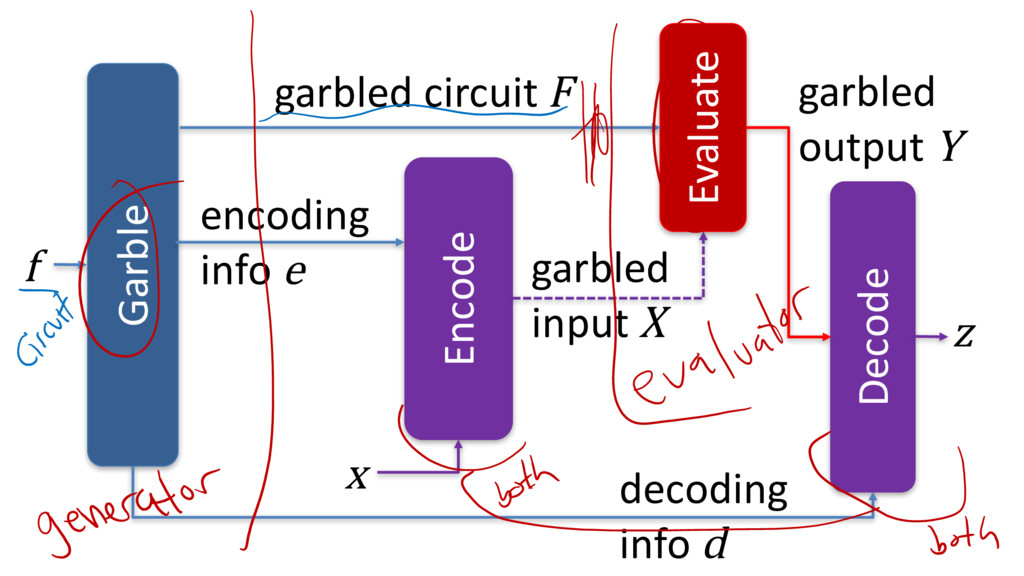
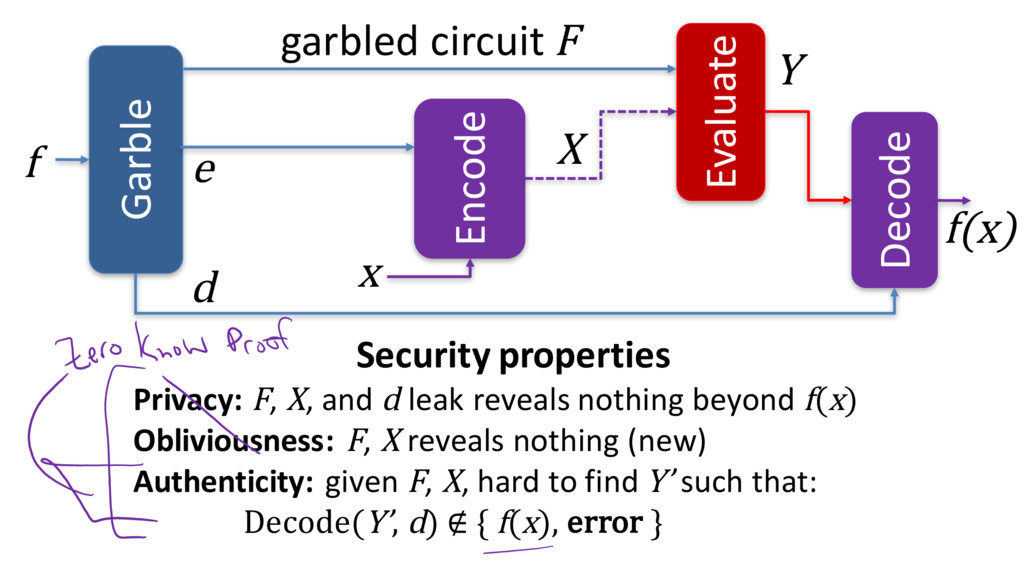
Garble Encode Evaluate Decode f garbled circuit F encoding info
e garbled input X garbled output Y z decoding info d x -
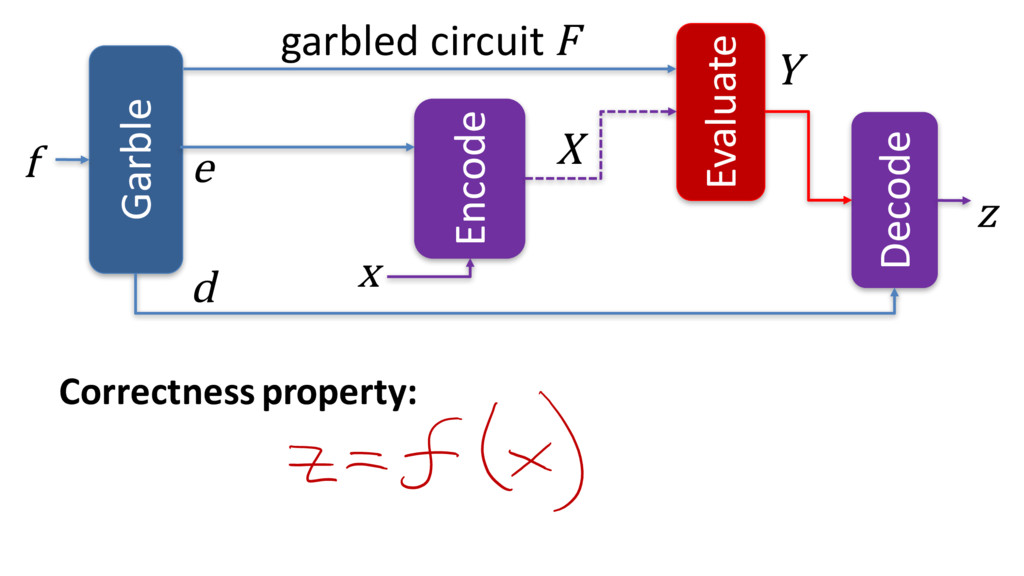
Garble Encode Evaluate Decode f garbled circuit F e X
Y z d x Correctness property: -
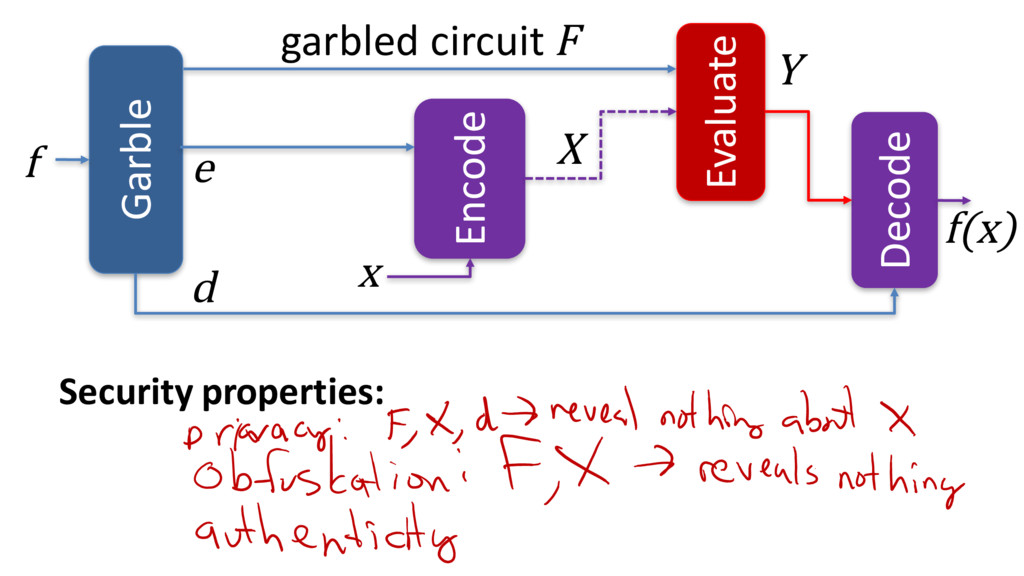
Garble Encode Evaluate Decode f garbled circuit F e X
Y f(x) d x Security properties: -
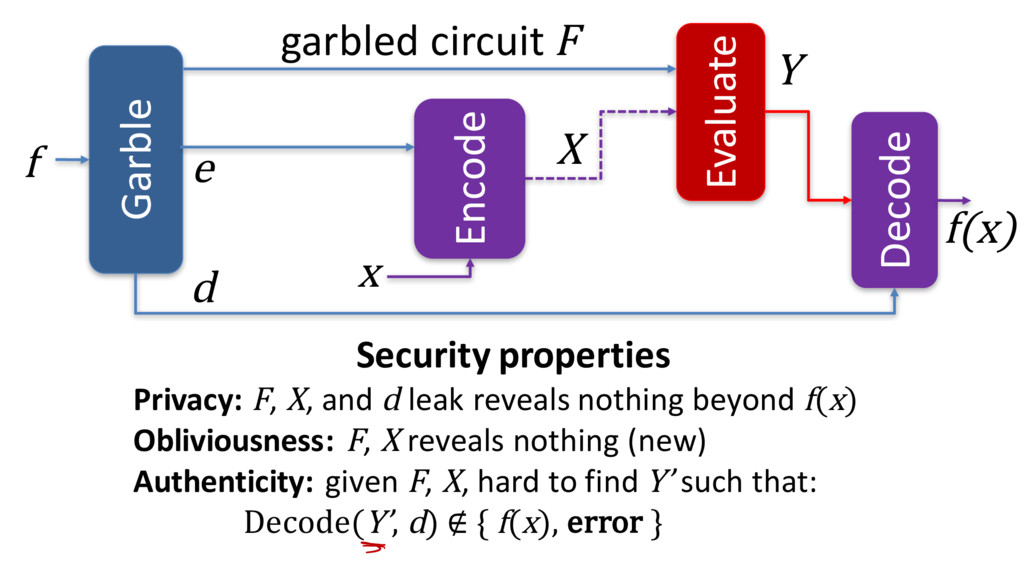
Garble Encode Evaluate Decode f garbled circuit F e X
Y f(x) d x Security properties Privacy: F, X, and d leak reveals nothing beyond f(x) Obliviousness: F, X reveals nothing (new) Authenticity: given F, X, hard to find Y’ such that: Decode(Y’, d) ∉ { f(x), error } -
Garble Encode Evaluate Decode f garbled circuit F e X
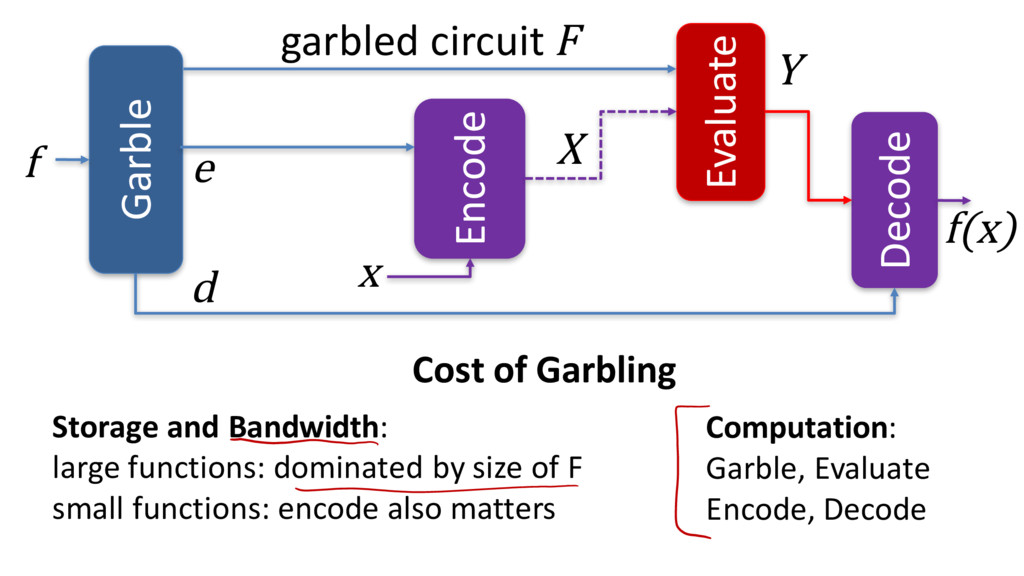
Y f(x) d x Cost of Garbling Storage and Bandwidth: large functions: dominated by size of F small functions: encode also matters Computation: Garble, Evaluate Encode, Decode -
Yao’s Garbling Scheme? FOCS 1982 FOCS 1986 Neither paper (or
any other by Yao) actually describes Yao’s Garbled Circuits -
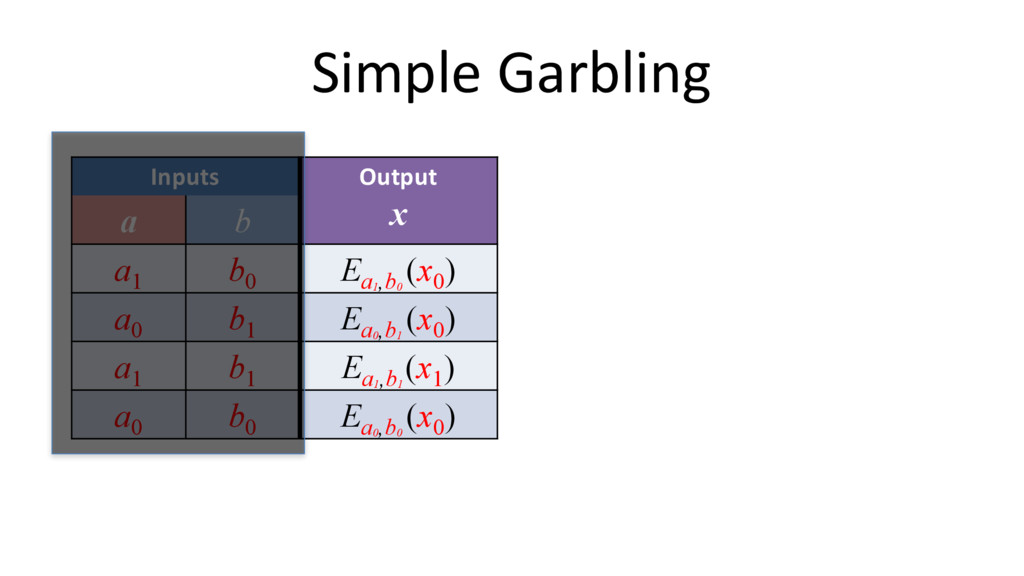
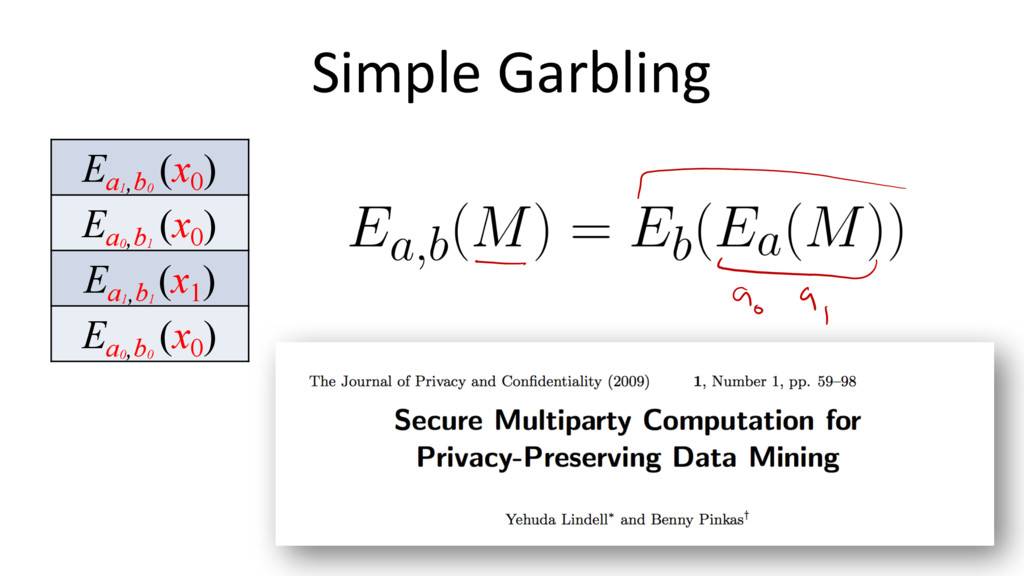
Inputs Output x a b a1 b0 Ea1 ,b0 (x0
) a0 b1 Ea0 ,b1 (x0 ) a1 b1 Ea1 ,b1 (x1 ) a0 b0 Ea0 ,b0 (x0 ) Simple Garbling -
Ea1 ,b0 (x0 ) Ea0 ,b1 (x0 ) Ea1 ,b1
(x1 ) Ea0 ,b0 (x0 ) Simple Garbling -
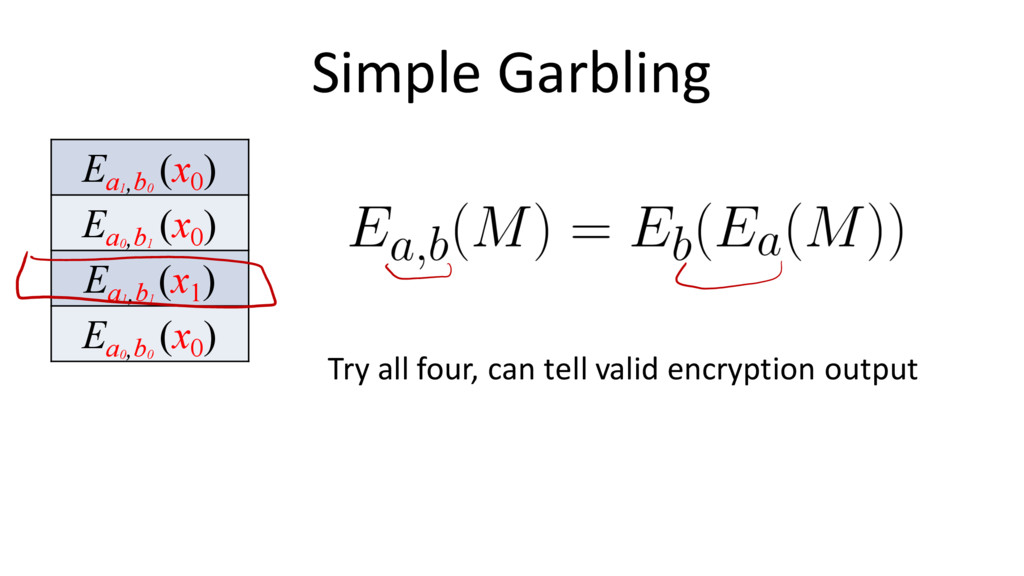
Ea1 ,b0 (x0 ) Ea0 ,b1 (x0 ) Ea1 ,b1
(x1 ) Ea0 ,b0 (x0 ) Simple Garbling Try all four, can tell valid encryption output -
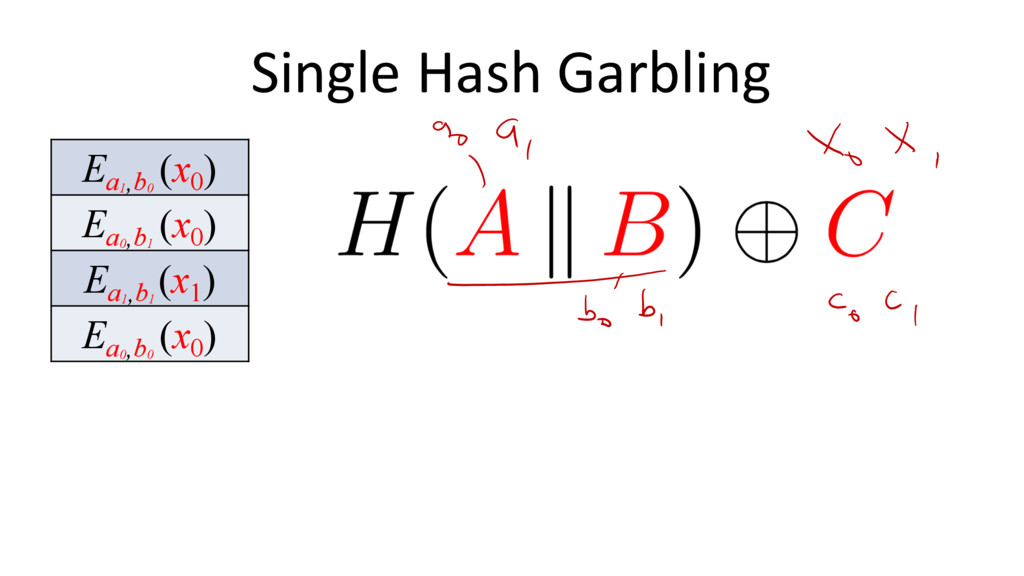
Ea1 ,b0 (x0 ) Ea0 ,b1 (x0 ) Ea1 ,b1
(x1 ) Ea0 ,b0 (x0 ) Single Hash Garbling -
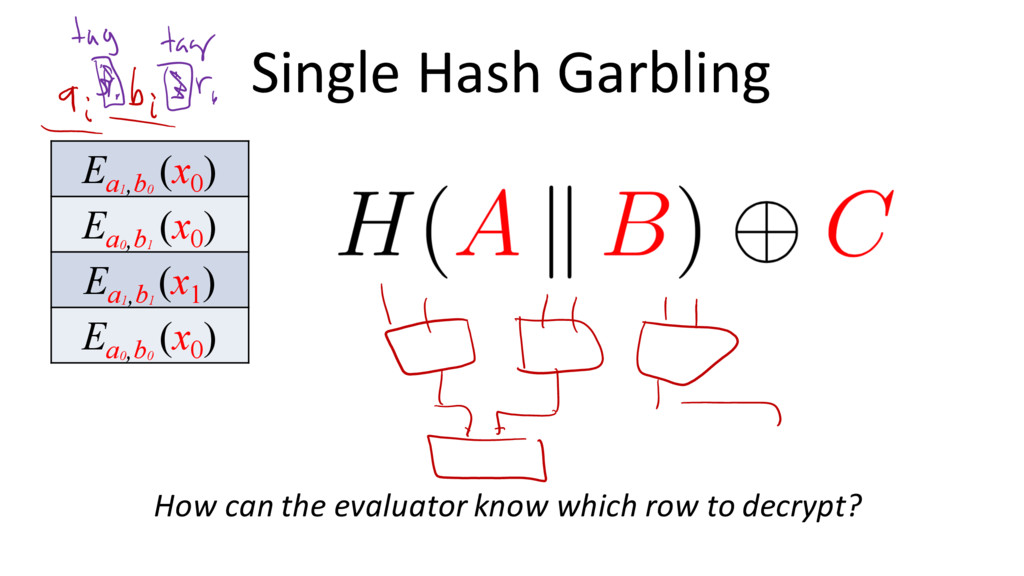
Ea1 ,b0 (x0 ) Ea0 ,b1 (x0 ) Ea1 ,b1
(x1 ) Ea0 ,b0 (x0 ) Single Hash Garbling How can the evaluator know which row to decrypt? -
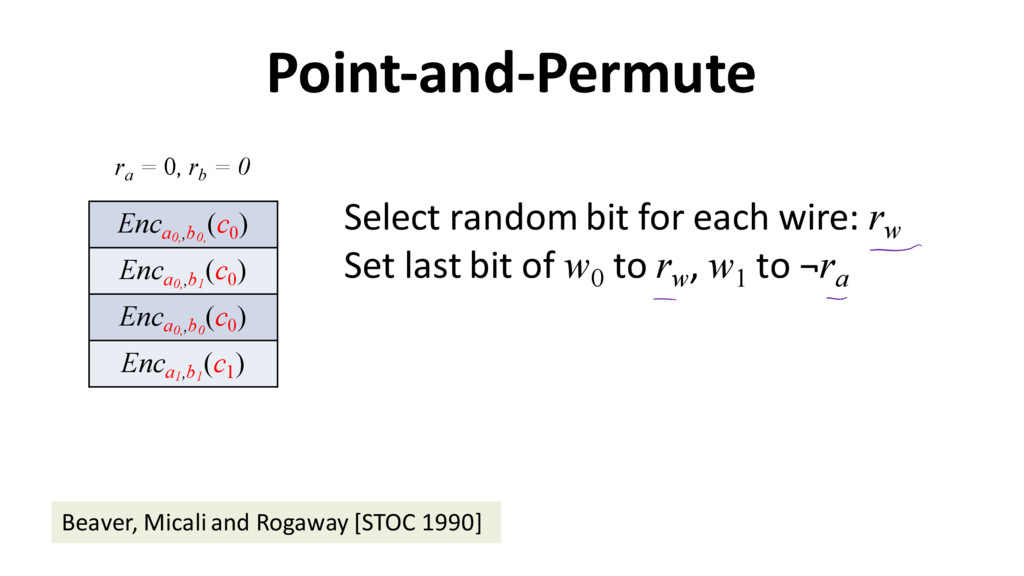
Point-and-Permute Enca0,,b0, (c0 ) Enca0,,b1 (c0 ) Enca0,,b0 (c0 )
Enca1,b1 (c1 ) Beaver, Micali and Rogaway [STOC 1990] Select random bit for each wire: rw Set last bit of w0 to rw , w1 to ¬ra ra = 0, rb = 0 -
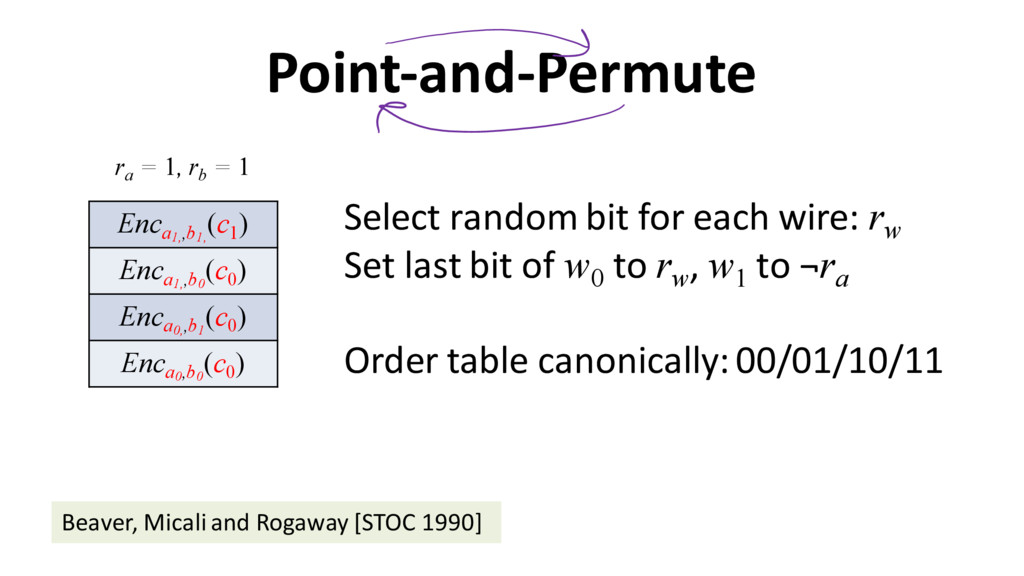
Point-and-Permute Enca1,,b1, (c1 ) Enca1,,b0 (c0 ) Enca0,,b1 (c0 )
Enca0,b0 (c0 ) Beaver, Micali and Rogaway [STOC 1990] Select random bit for each wire: rw Set last bit of w0 to rw , w1 to ¬ra Order table canonically: 00/01/10/11 ra = 1, rb = 1 -
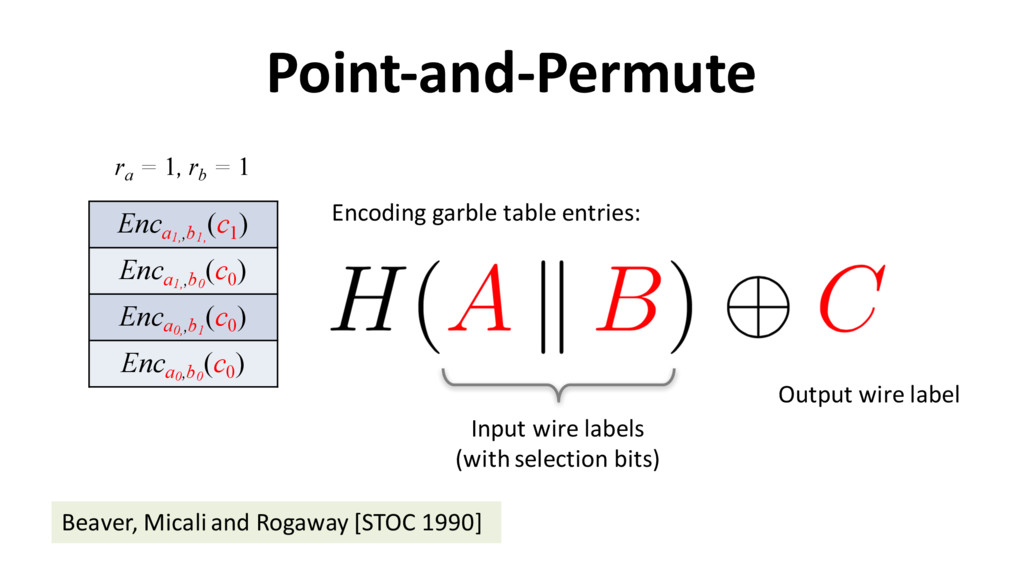
Point-and-Permute Encoding garble table entries: Input wire labels (with selection
bits) Output wire label Beaver, Micali and Rogaway [STOC 1990] Enca1,,b1, (c1 ) Enca1,,b0 (c0 ) Enca0,,b1 (c0 ) Enca0,b0 (c0 ) ra = 1, rb = 1 -
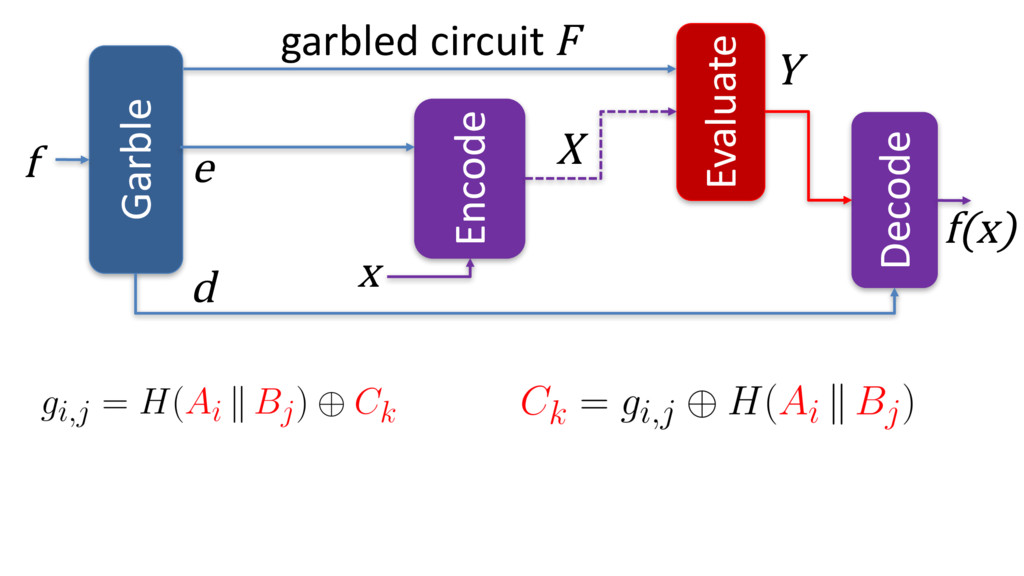
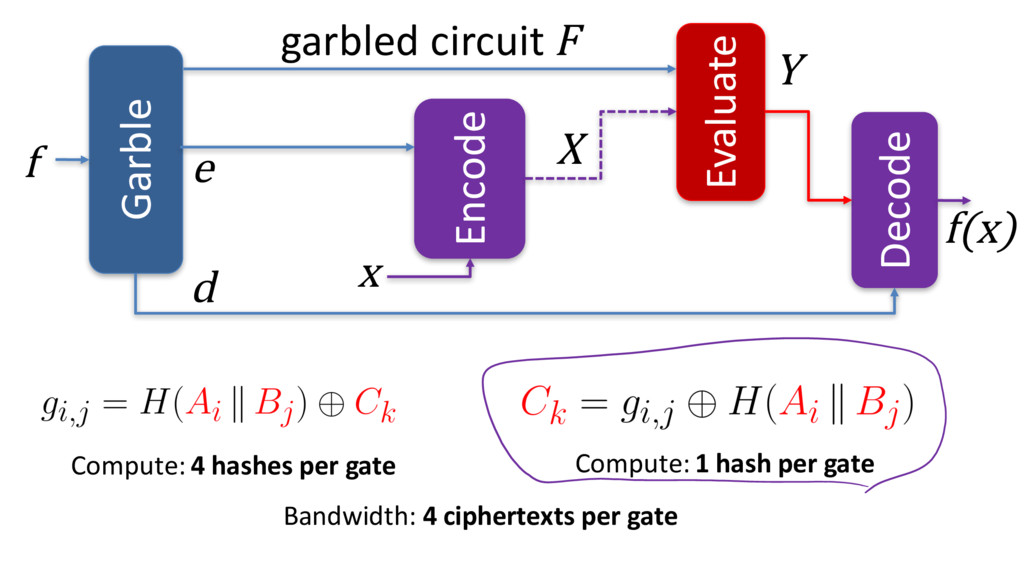
Garble Encode Evaluate Decode f garbled circuit F e X
Y f(x) d x Bandwidth: 4 ciphertexts per gate Compute: 4 hashes per gate Compute: 1 hash per gate -
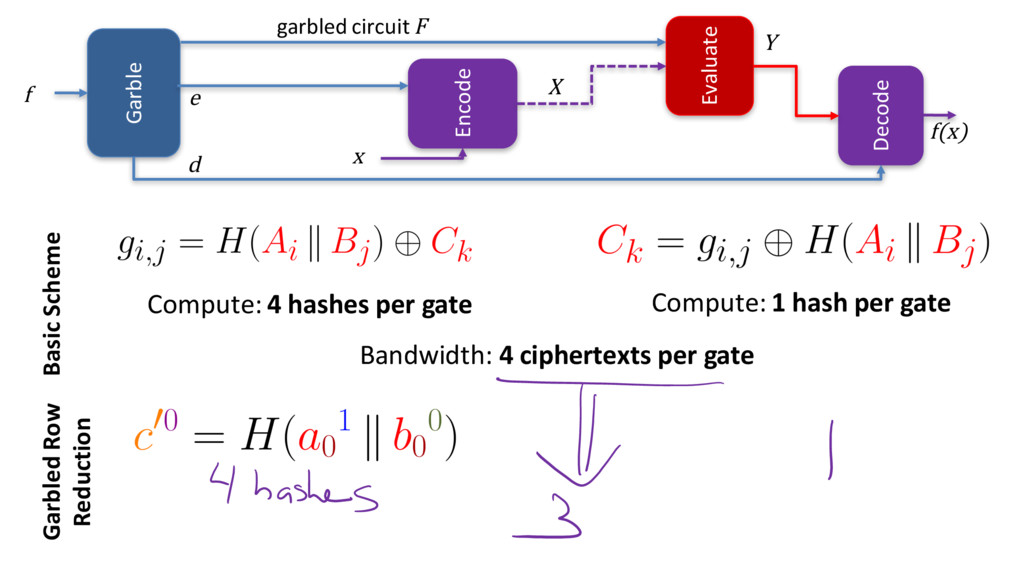
Garble Encode Evaluate Decode f garbled circuit F e X
Y f(x) d x Bandwidth: 4 ciphertexts per gate Compute: 4 hashes per gate Compute: 1 hash per gate Basic Scheme Garbled Row Reduction -
Garble Encode Evaluate Decode f garbled circuit F e X
Y f(x) d x Bandwidth: 4 ciphertexts per gate Compute: 4 hashes per gate Compute: 1 hash per gate Basic Scheme Garbled Row Reduction Bandwidth: 3 ciphertexts per gate -
Free-XOR Kolesnikov and Schneider [2008] Global generator secret XOR are
free! No ciphertexts or encryption needed. -
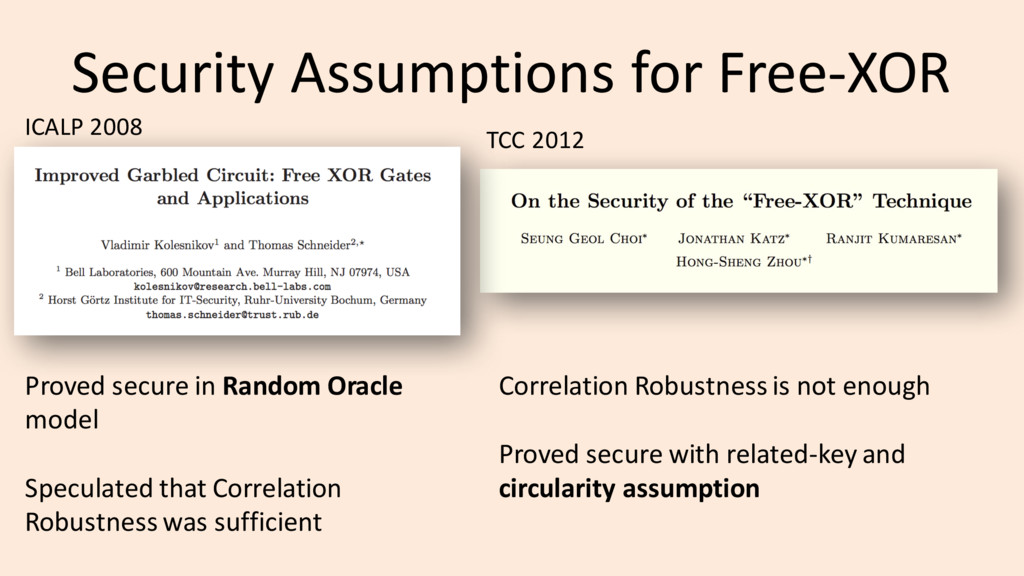
Security Assumptions for Free-XOR ICALP 2008 Proved secure in Random
Oracle model Speculated that Correlation Robustness was sufficient TCC 2012 Correlation Robustness is not enough Proved secure with related-key and circularity assumption -
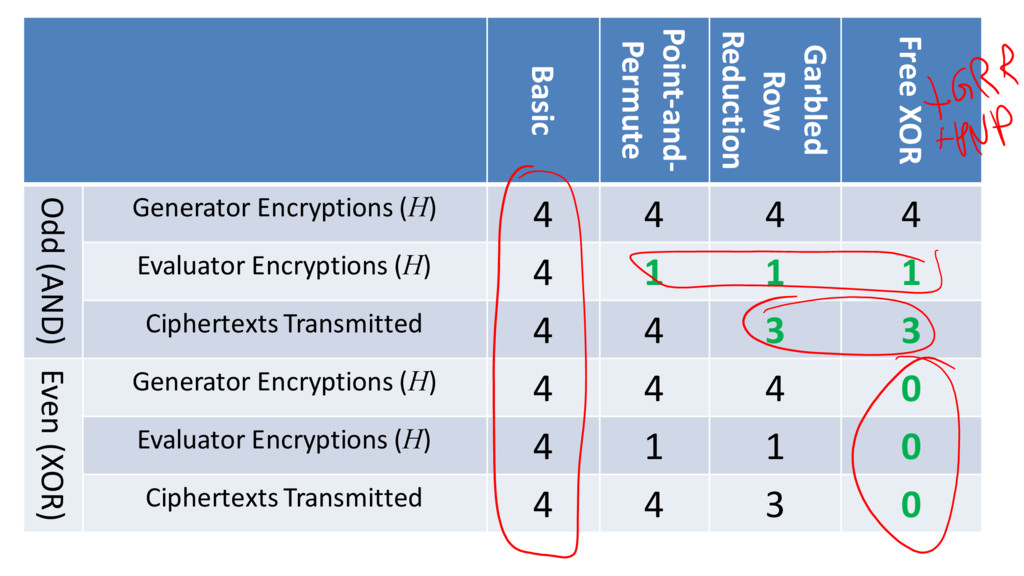
Basic Point-and- Permute Garbled Row Reduction Free XOR Odd (AND)
Generator Encryptions (H) 4 4 4 4 Evaluator Encryptions (H) 4 1 1 1 Ciphertexts Transmitted 4 4 3 3 Even (XOR) Generator Encryptions (H) 4 4 4 0 Evaluator Encryptions (H) 4 1 1 0 Ciphertexts Transmitted 4 4 3 0 -
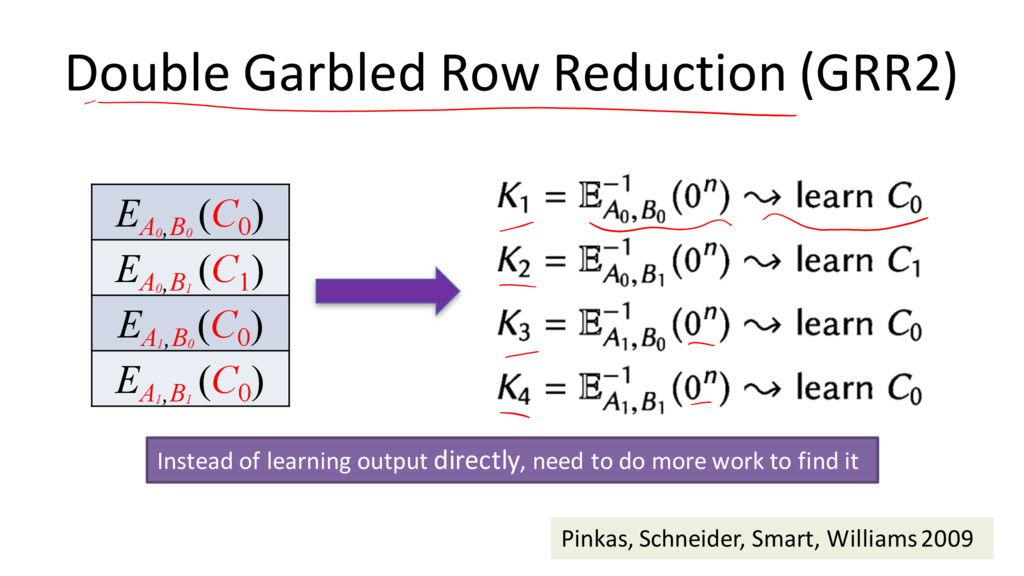
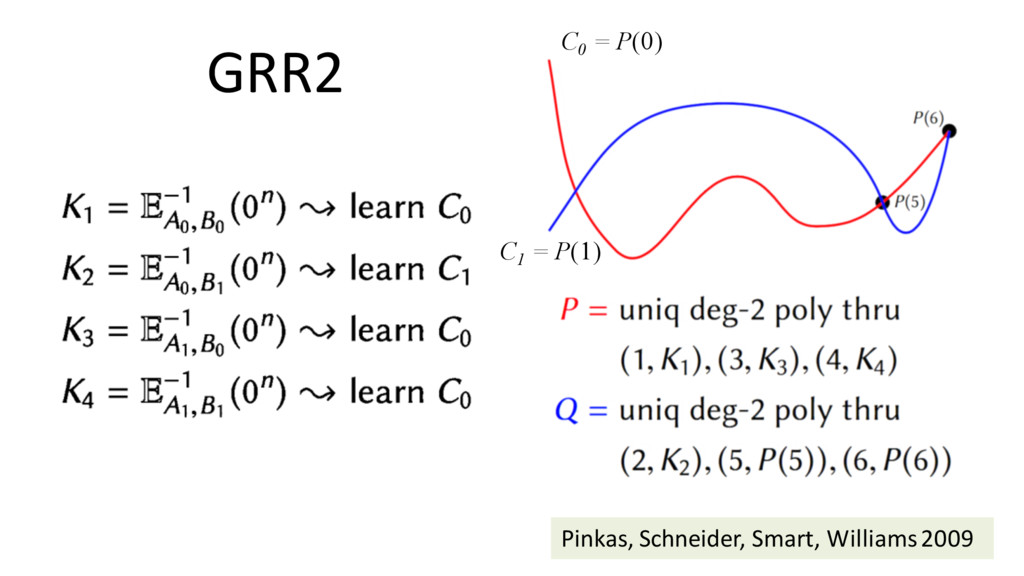
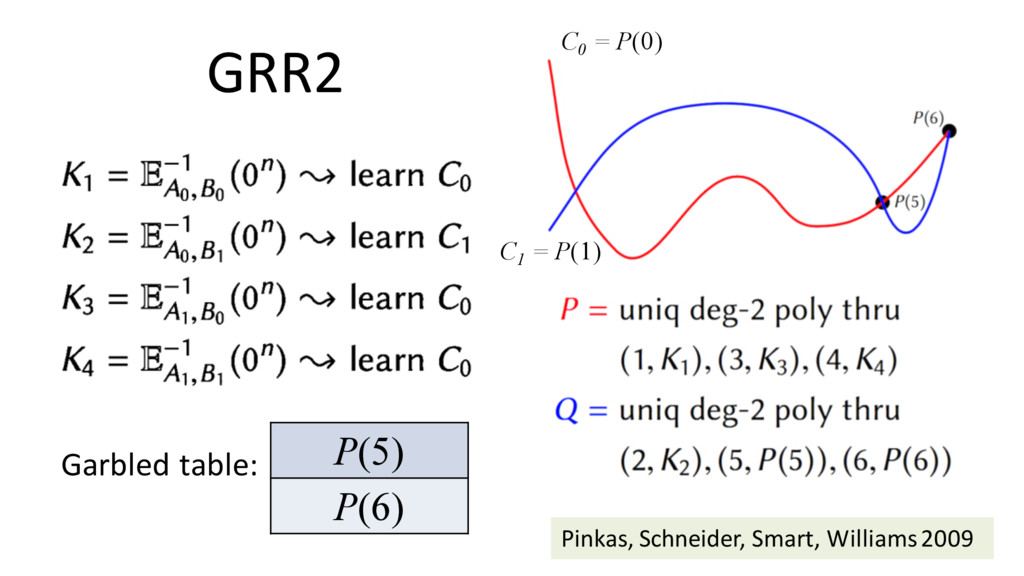
Double Garbled Row Reduction (GRR2) Pinkas, Schneider, Smart, Williams 2009
EA0 ,B0 (C0 ) EA0 ,B1 (C1 ) EA1 ,B0 (C0 ) EA1 ,B1 (C0 ) Instead of learning output directly, need to do more work to find it -
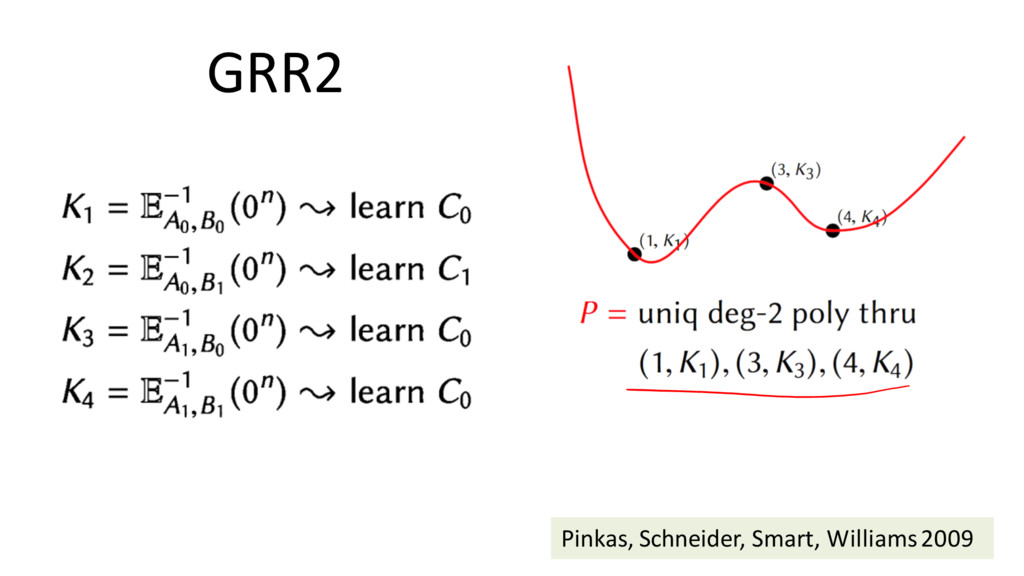
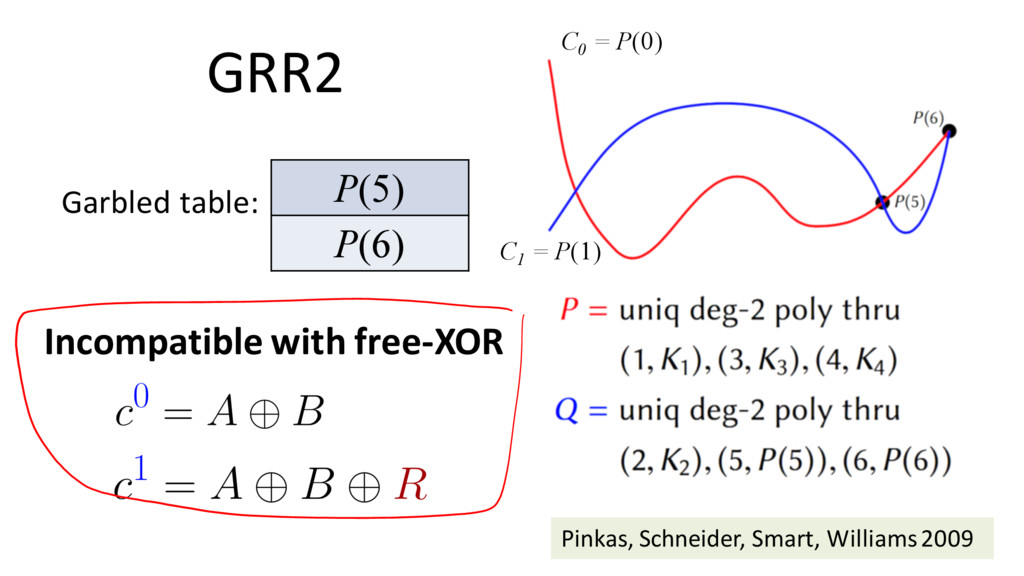
Pinkas, Schneider, Smart, Williams 2009 GRR2 C0 = P(0) C1
= P(1) P(5) P(6) Garbled table: -
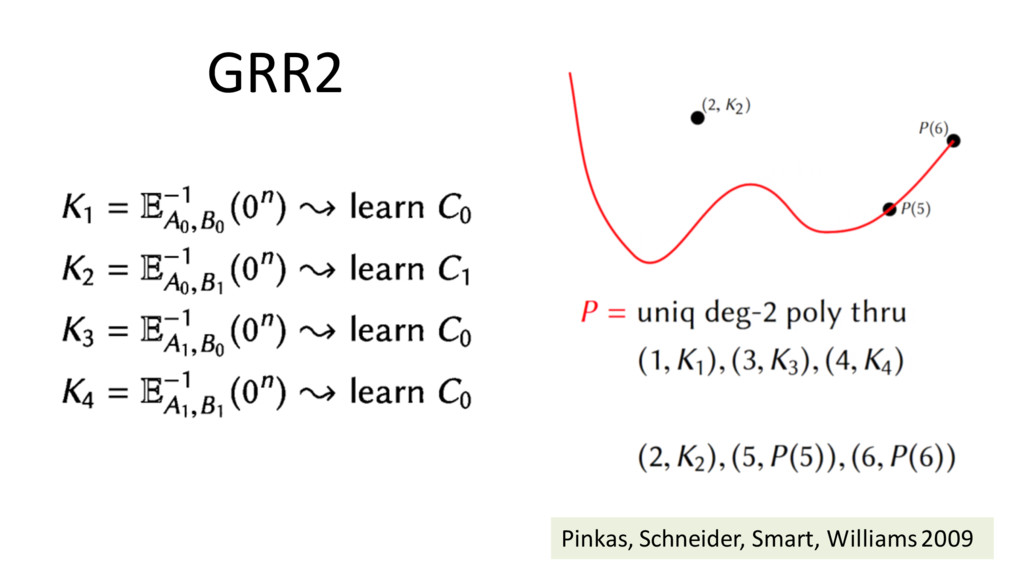
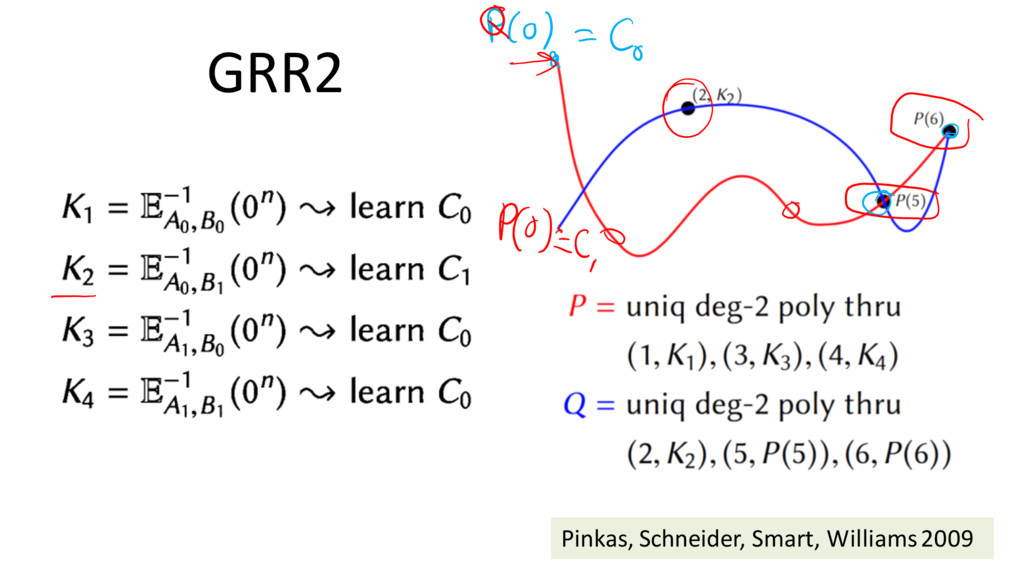
Pinkas, Schneider, Smart, Williams 2009 GRR2 C0 = P(0) C1
= P(1) P(5) P(6) Garbled table: Incompatible with free-XOR -
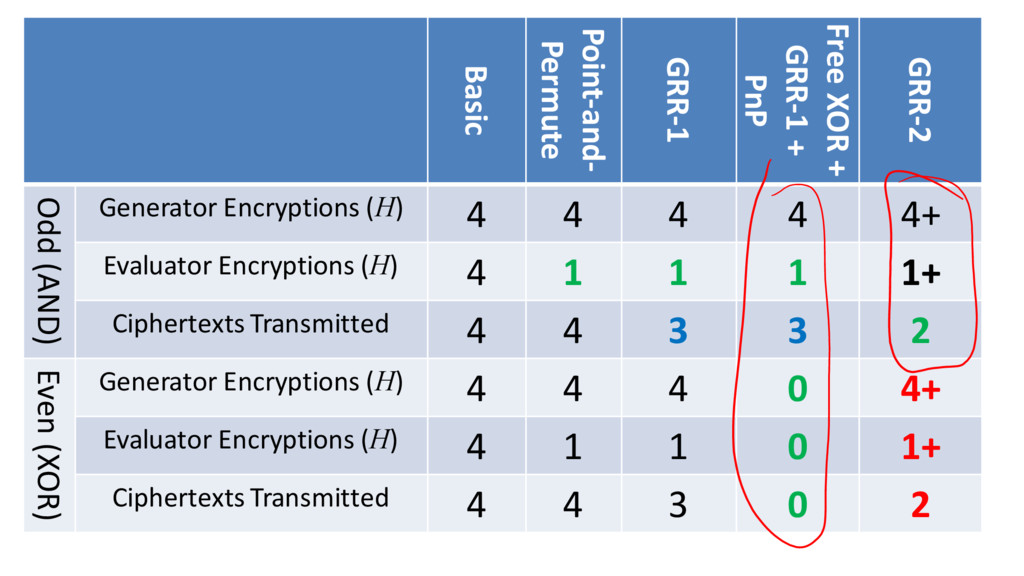
Basic Point-and- Permute GRR-1 Free XOR + GRR-1 + PnP
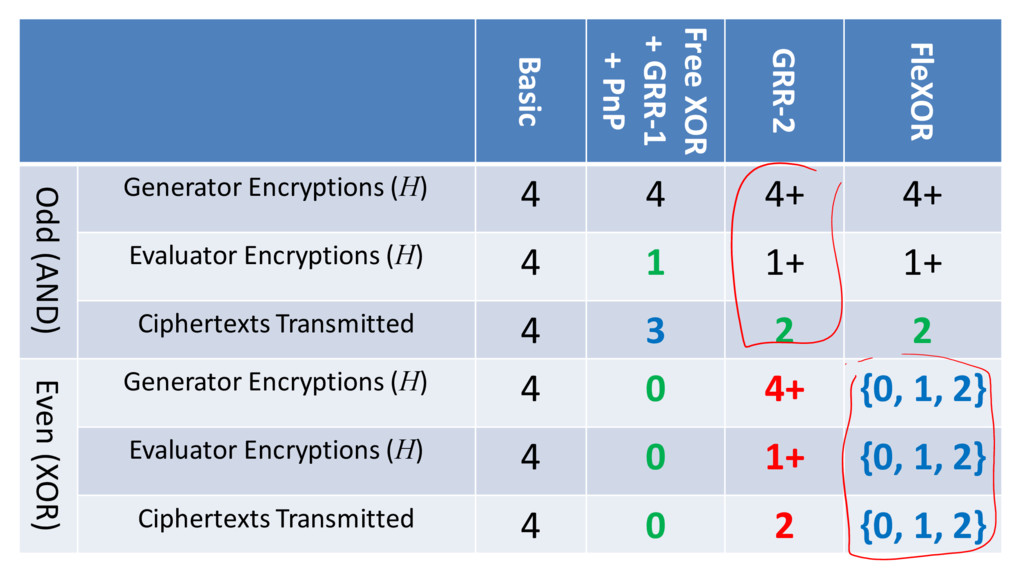
GRR-2 Odd (AND) Generator Encryptions (H) 4 4 4 4 4+ Evaluator Encryptions (H) 4 1 1 1 1+ Ciphertexts Transmitted 4 4 3 3 2 Even (XOR) Generator Encryptions (H) 4 4 4 0 4+ Evaluator Encryptions (H) 4 1 1 0 1+ Ciphertexts Transmitted 4 4 3 0 2 -
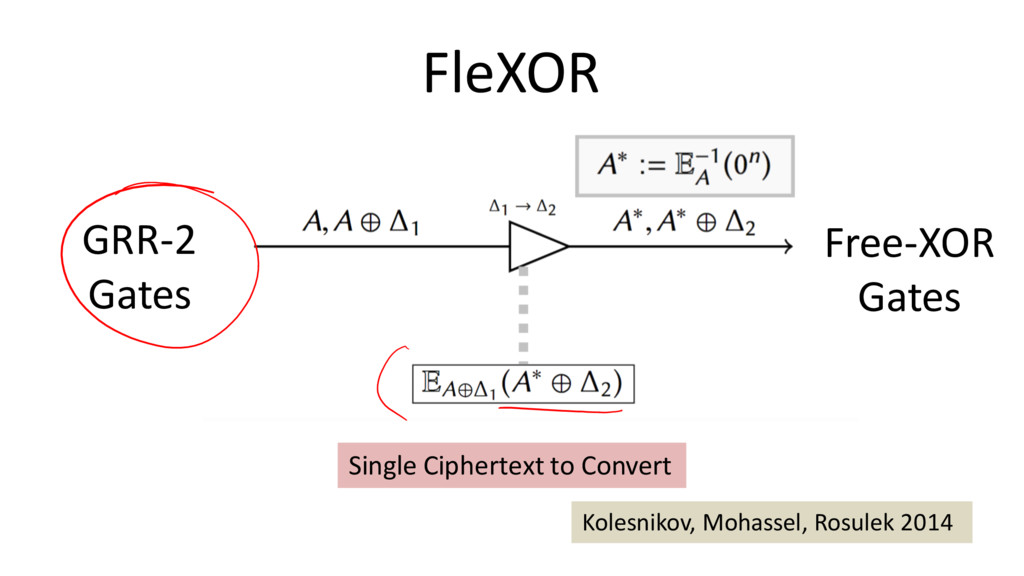
FleXOR Kolesnikov, Mohassel, Rosulek 2014 S GRR-2 Gates Free-XOR Gates
Single Ciphertext to Convert -
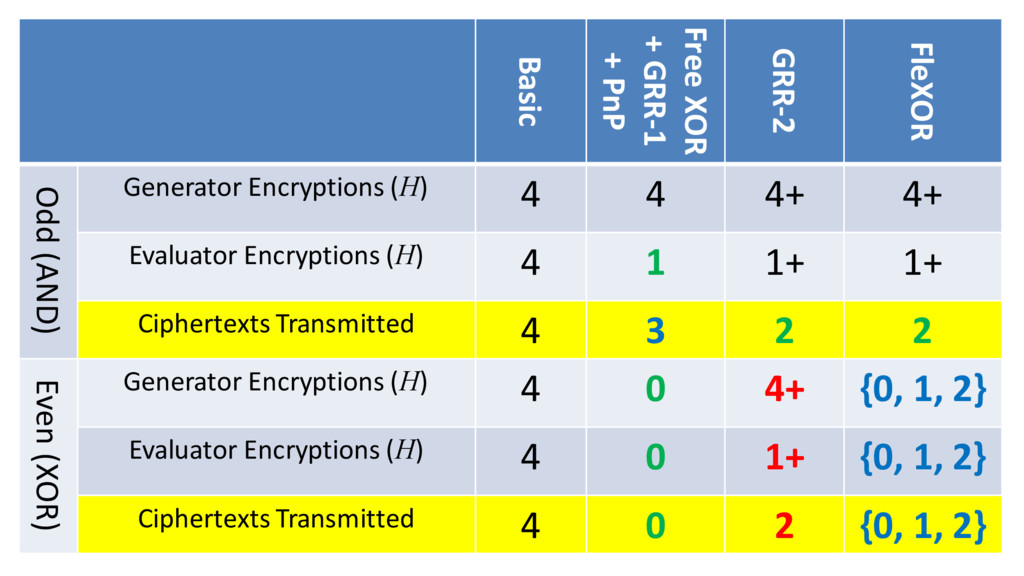
Basic Free XOR + GRR-1 + PnP GRR-2 FleXOR Odd
(AND) Generator Encryptions (H) 4 4 4+ 4+ Evaluator Encryptions (H) 4 1 1+ 1+ Ciphertexts Transmitted 4 3 2 2 Even (XOR) Generator Encryptions (H) 4 0 4+ {0, 1, 2} Evaluator Encryptions (H) 4 0 1+ {0, 1, 2} Ciphertexts Transmitted 4 0 2 {0, 1, 2} -
Basic Free XOR + GRR-1 + PnP GRR-2 FleXOR Odd
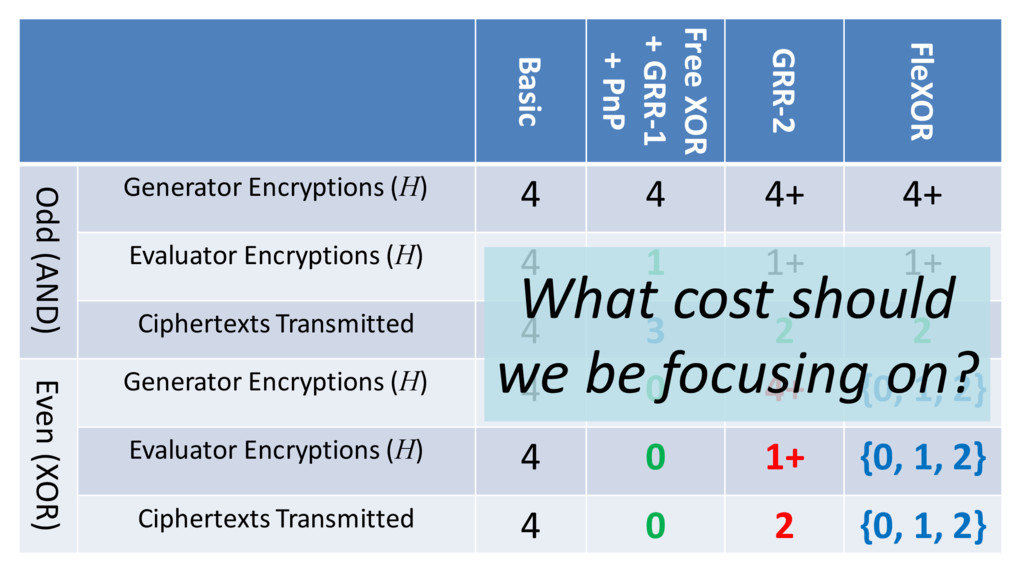
(AND) Generator Encryptions (H) 4 4 4+ 4+ Evaluator Encryptions (H) 4 1 1+ 1+ Ciphertexts Transmitted 4 3 2 2 Even (XOR) Generator Encryptions (H) 4 0 4+ {0, 1, 2} Evaluator Encryptions (H) 4 0 1+ {0, 1, 2} Ciphertexts Transmitted 4 0 2 {0, 1, 2} What cost should we be focusing on? -
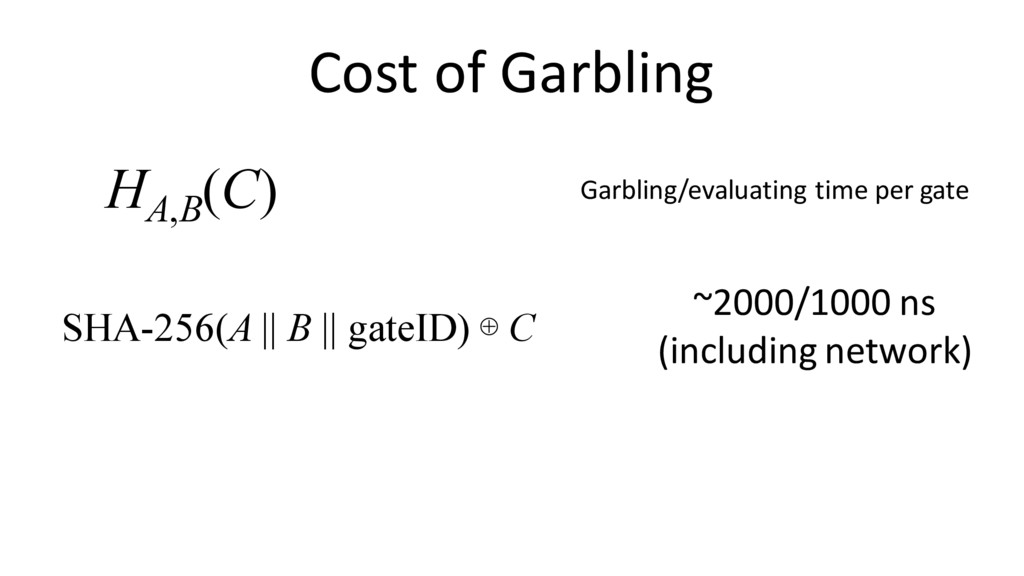
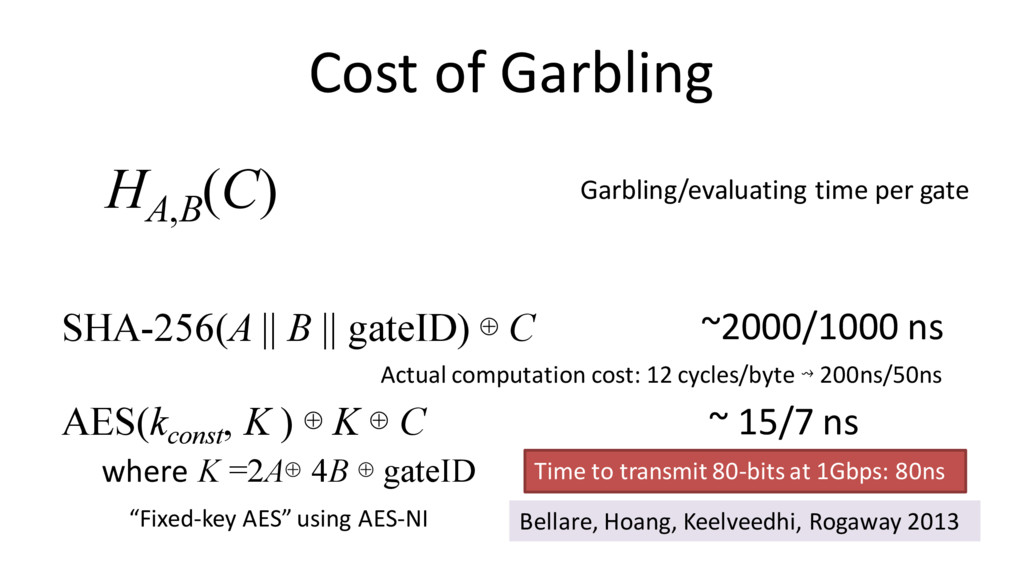
Cost of Garbling HA,B (C) SHA-256(A || B || gateID)
⊕ C ~2000/1000 ns (including network) Garbling/evaluating time per gate -
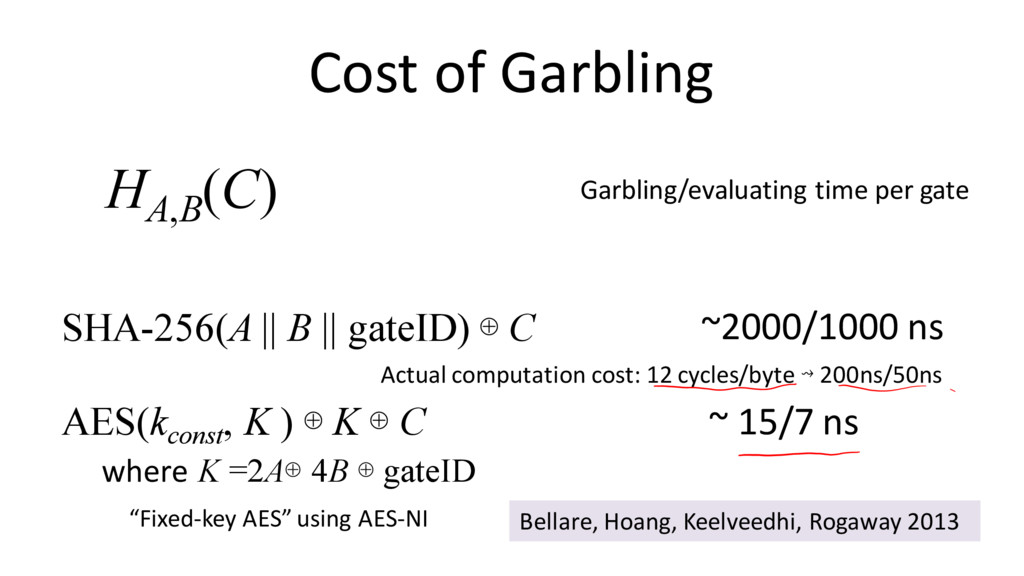
Cost of Garbling HA,B (C) AES(kconst , K ) ⊕
K ⊕ C where K =2A⊕ 4B ⊕ gateID SHA-256(A || B || gateID) ⊕ C ~2000/1000 ns Bellare, Hoang, Keelveedhi, Rogaway 2013 “Fixed-key AES” using AES-NI ~ 15/7 ns Garbling/evaluating time per gate Actual computation cost: 12 cycles/byte ⇝ 200ns/50ns -
Cost of Garbling HA,B (C) AES(kconst , K ) ⊕
K ⊕ C where K =2A⊕ 4B ⊕ gateID SHA-256(A || B || gateID) ⊕ C ~2000/1000 ns Bellare, Hoang, Keelveedhi, Rogaway 2013 “Fixed-key AES” using AES-NI ~ 15/7 ns Garbling/evaluating time per gate Time to transmit 80-bits at 1Gbps: 80ns Actual computation cost: 12 cycles/byte ⇝ 200ns/50ns -
Basic Free XOR + GRR-1 + PnP GRR-2 FleXOR Odd
(AND) Generator Encryptions (H) 4 4 4+ 4+ Evaluator Encryptions (H) 4 1 1+ 1+ Ciphertexts Transmitted 4 3 2 2 Even (XOR) Generator Encryptions (H) 4 0 4+ {0, 1, 2} Evaluator Encryptions (H) 4 0 1+ {0, 1, 2} Ciphertexts Transmitted 4 0 2 {0, 1, 2} -
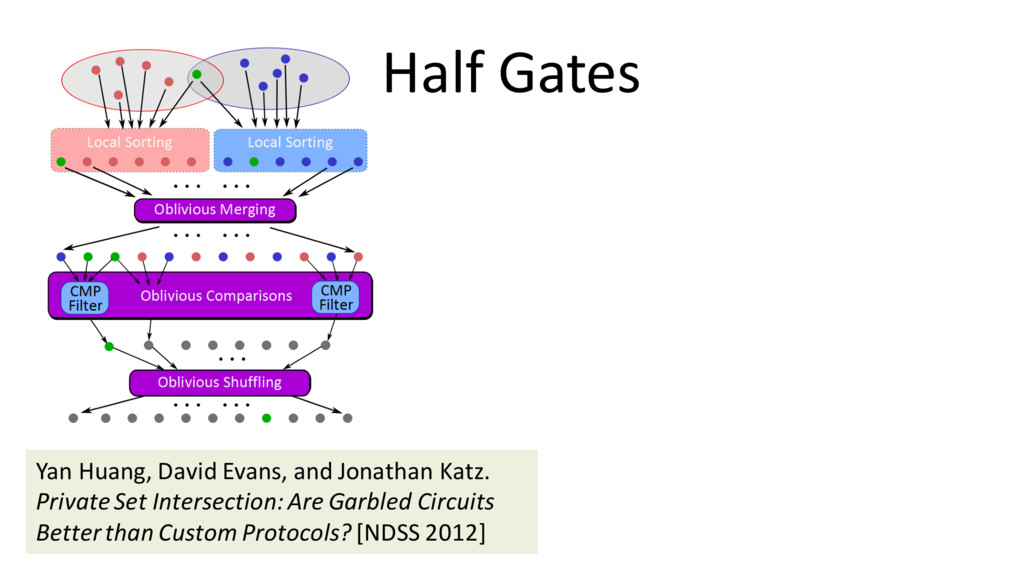
Half Gates Yan Huang, David Evans, and Jonathan Katz. Private
Set Intersection: Are Garbled Circuits Better than Custom Protocols? [NDSS 2012] -
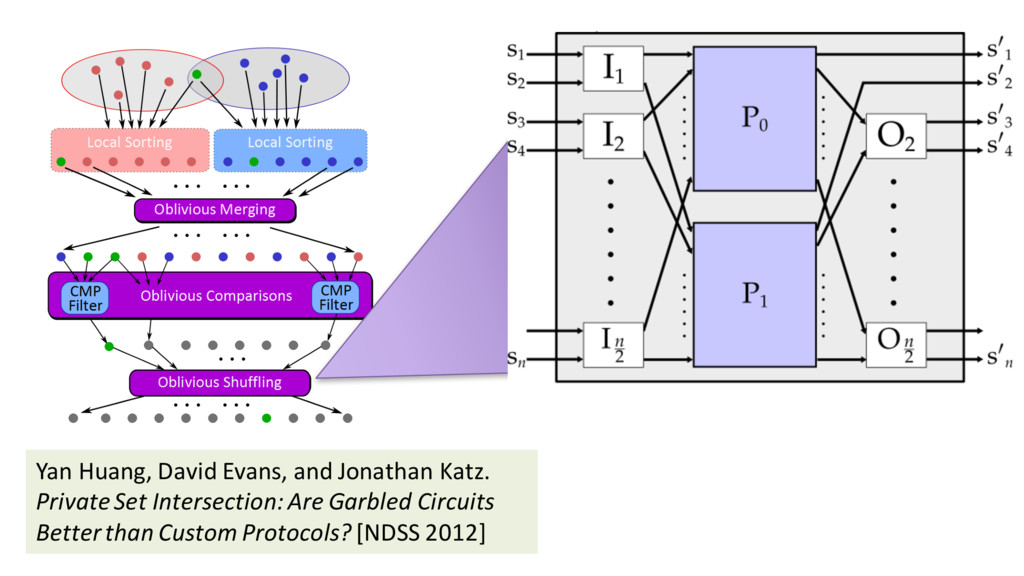
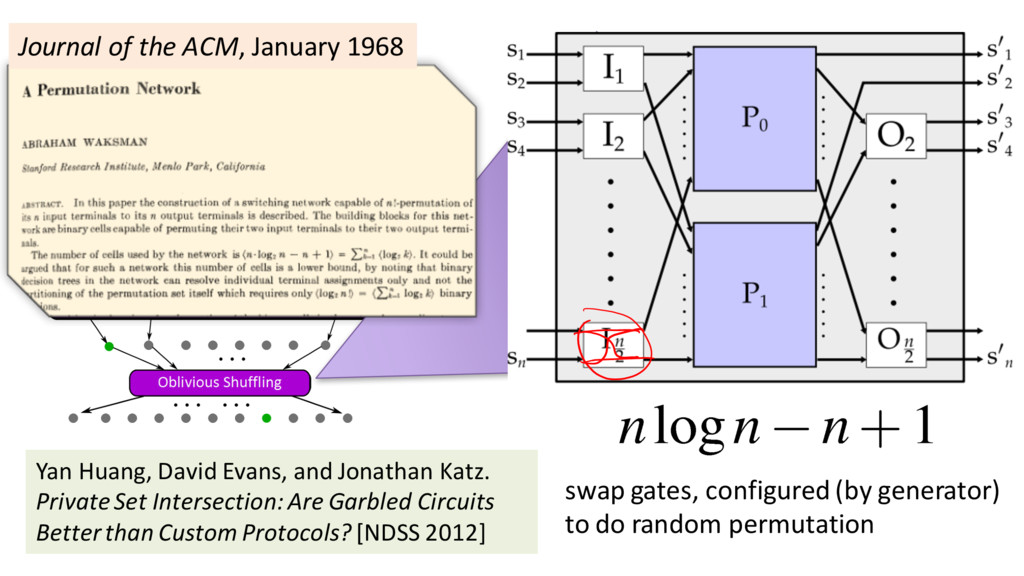
Yan Huang, David Evans, and Jonathan Katz. Private Set Intersection:
Are Garbled Circuits Better than Custom Protocols? [NDSS 2012] -
Yan Huang, David Evans, and Jonathan Katz. Private Set Intersection:
Are Garbled Circuits Better than Custom Protocols? [NDSS 2012] Journal of the ACM, January 1968 swap gates, configured (by generator) to do random permutation -
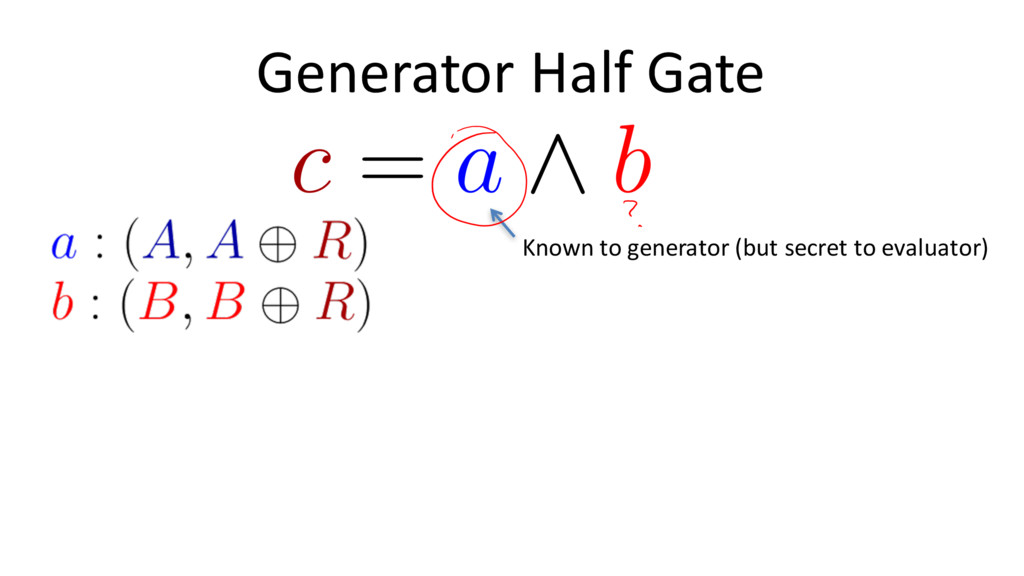
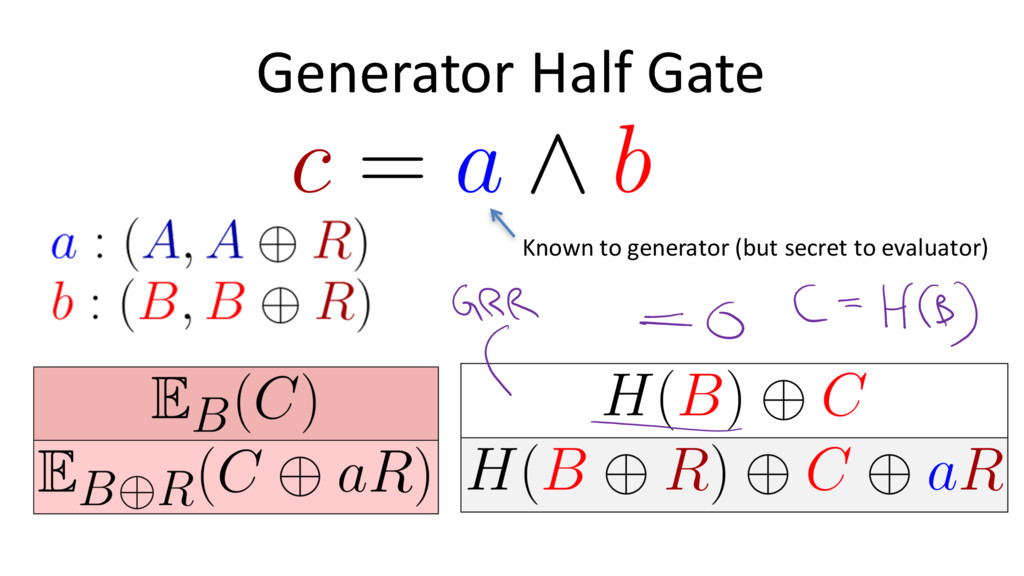
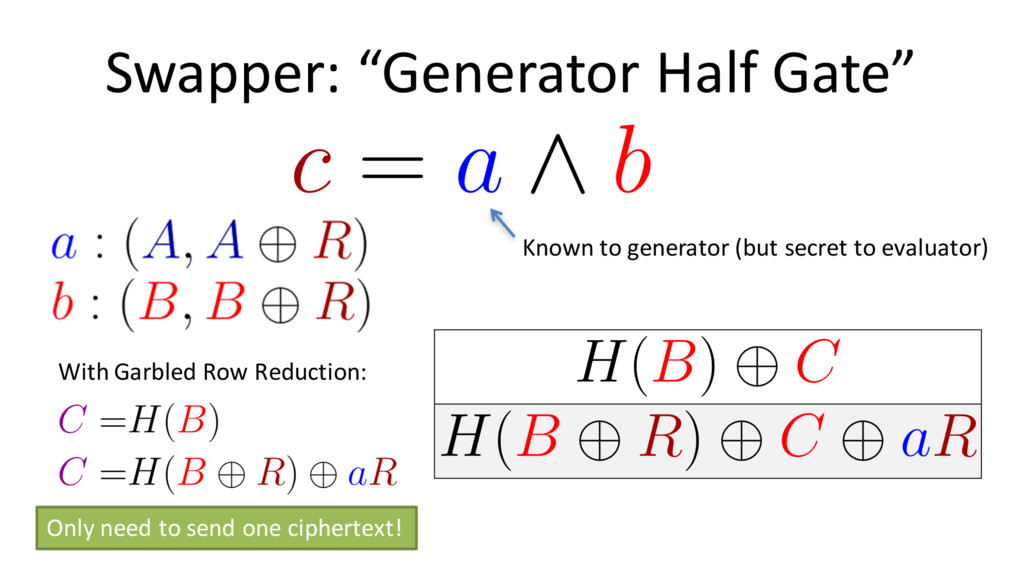
Swapper: “Generator Half Gate” Known to generator (but secret to
evaluator) With Garbled Row Reduction: Only need to send one ciphertext! -
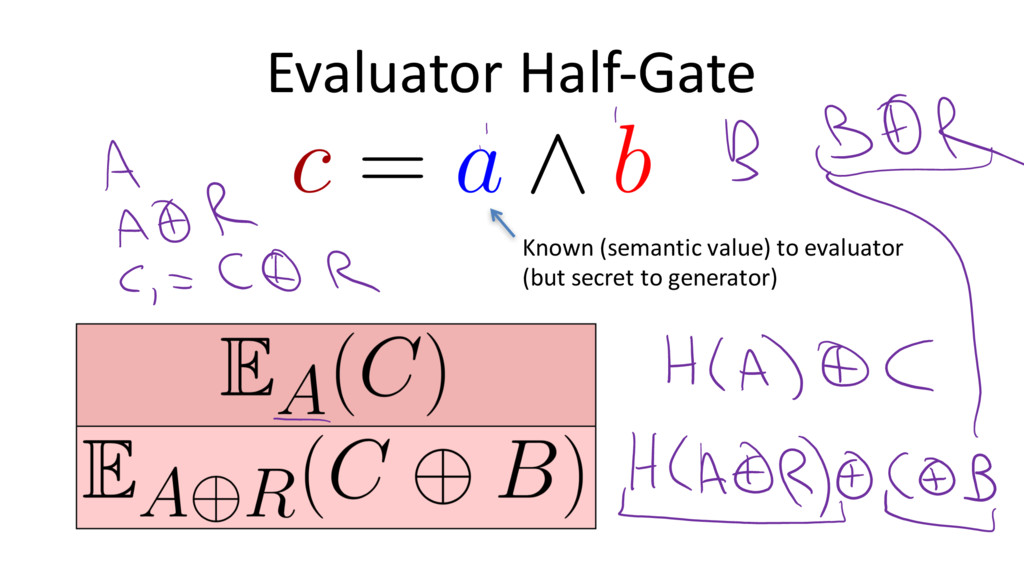
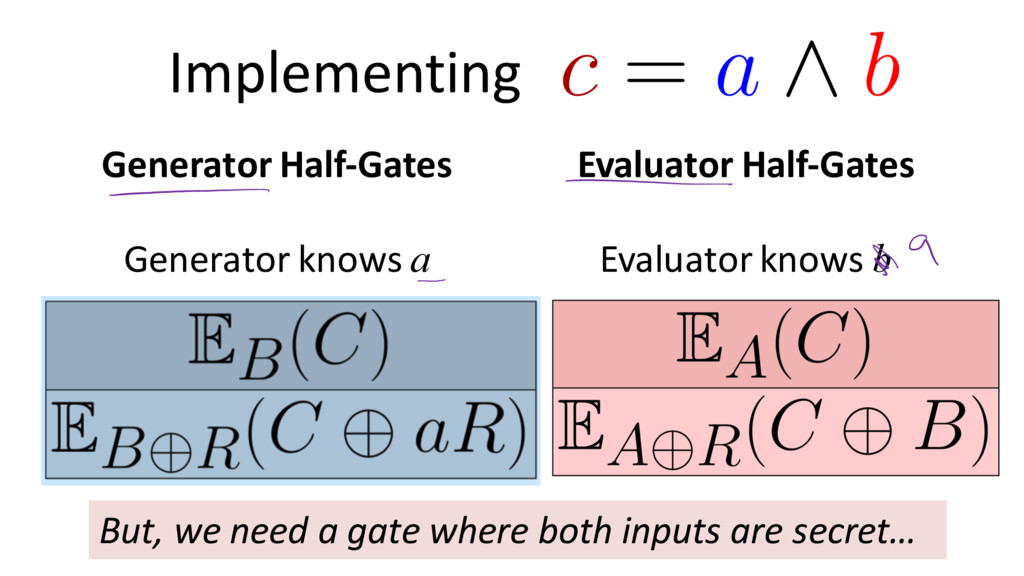
Generator Half-Gates Generator knows a Evaluator Half-Gates Evaluator knows b
Implementing But, we need a gate where both inputs are secret… -
Half + Half = Full Secret Gate random bit selected
by generator “leaked” unknown known unknown -
Half + Half = Full Secret Gate random bit selected
by generator “leaked” unknown known unknown -
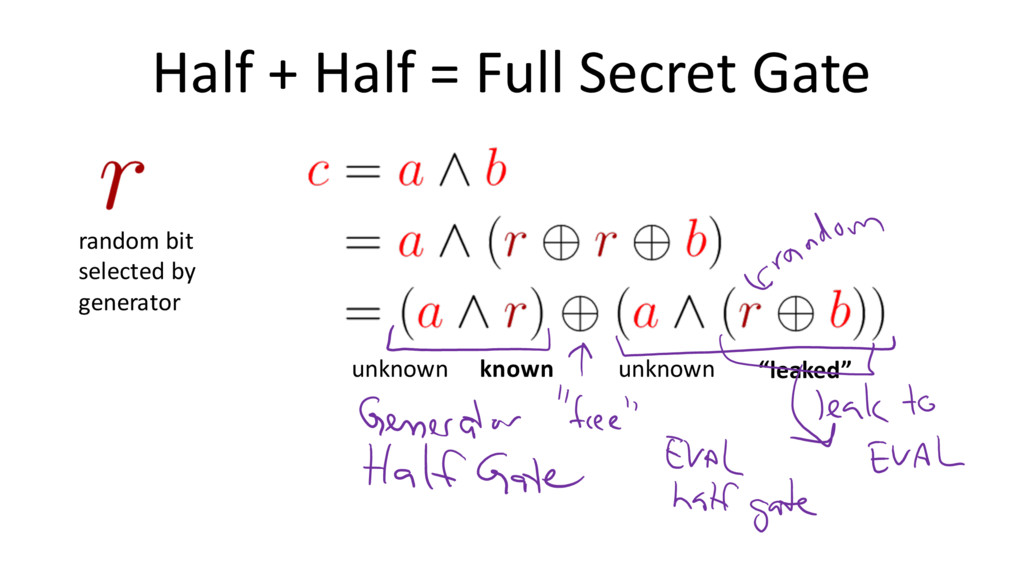
Half + Half = Full Secret Gate random bit selected
by generator “leaked” unknown known unknown -
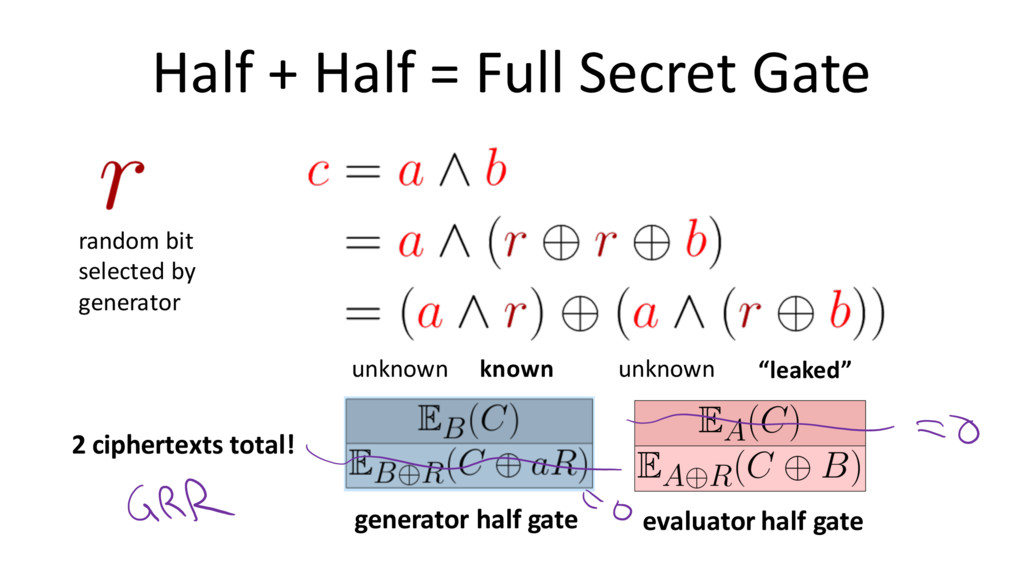
Half + Half = Full Secret Gate random bit selected
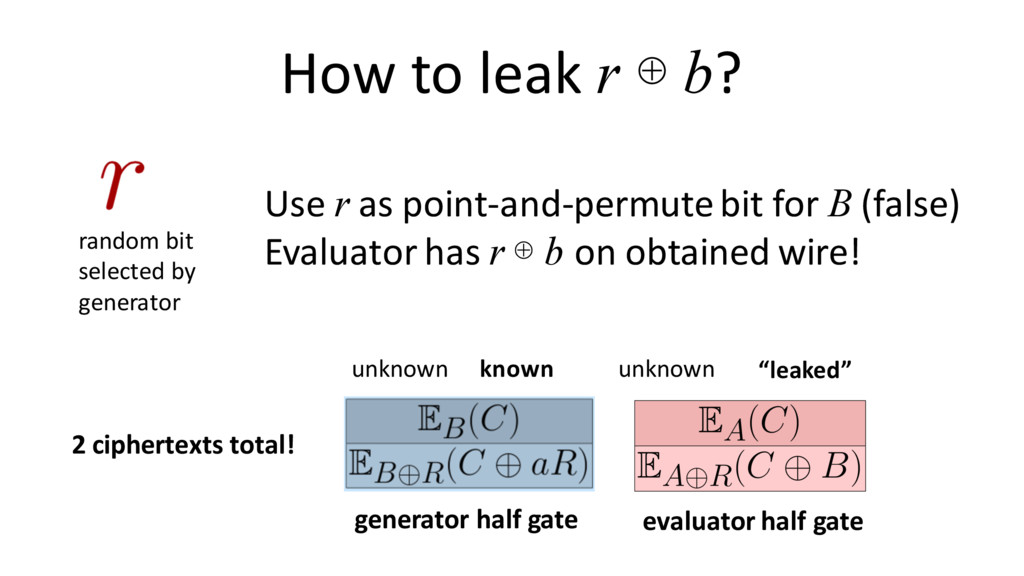
by generator generator half gate evaluator half gate “leaked” unknown known unknown 2 ciphertexts total! -
How to leak r ⊕ b? random bit selected by
generator generator half gate evaluator half gate “leaked” unknown known unknown 2 ciphertexts total! Use r as point-and-permute bit for B (false) Evaluator has r ⊕ b on obtained wire! -
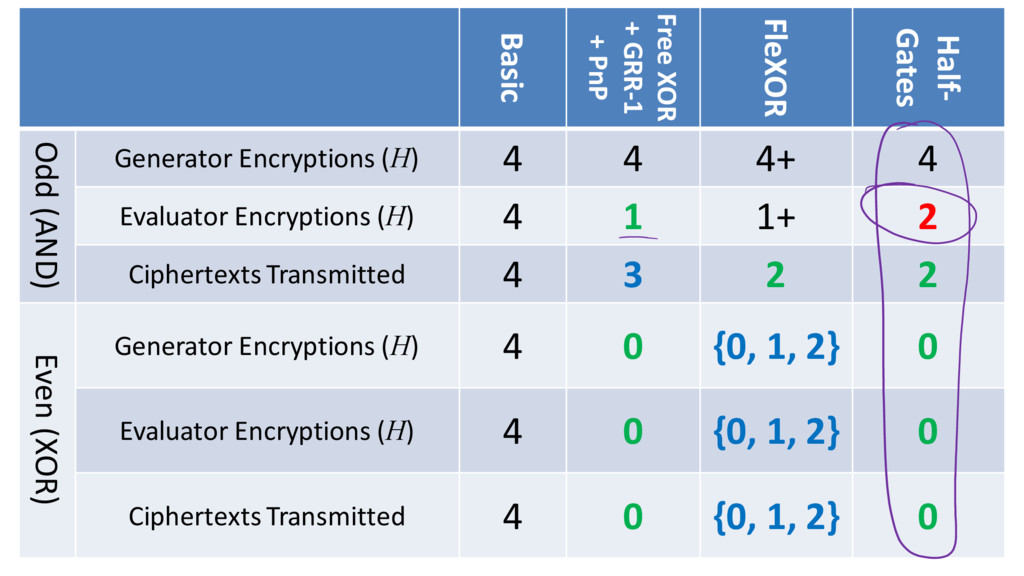
Basic Free XOR + GRR-1 + PnP FleXOR Half- Gates
Odd (AND) Generator Encryptions (H) 4 4 4+ 4 Evaluator Encryptions (H) 4 1 1+ 2 Ciphertexts Transmitted 4 3 2 2 Even (XOR) Generator Encryptions (H) 4 0 {0, 1, 2} 0 Evaluator Encryptions (H) 4 0 {0, 1, 2} 0 Ciphertexts Transmitted 4 0 {0, 1, 2} 0 -
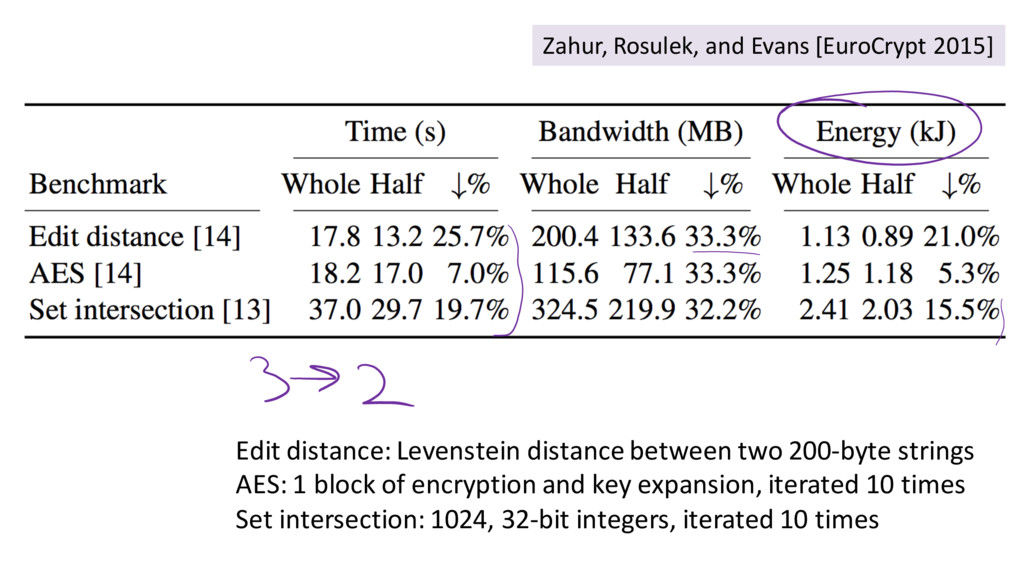
Edit distance: Levenstein distance between two 200-byte strings AES: 1
block of encryption and key expansion, iterated 10 times Set intersection: 1024, 32-bit integers, iterated 10 times Zahur, Rosulek, and Evans [EuroCrypt 2015] -
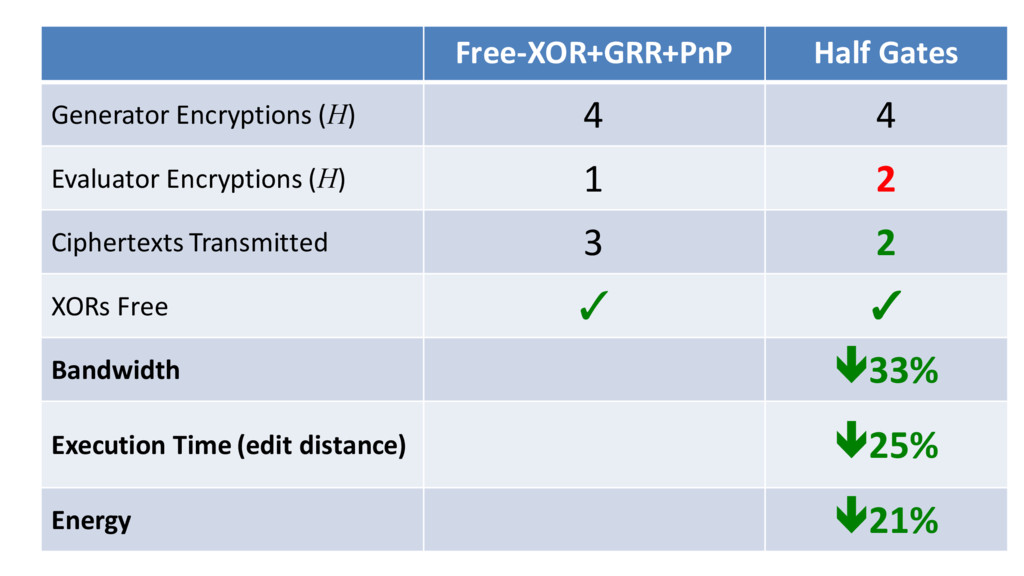
Free-XOR+GRR+PnP Half Gates Generator Encryptions (H) 4 4 Evaluator Encryptions
(H) 1 2 Ciphertexts Transmitted 3 2 XORs Free ✓ ✓ Bandwidth ê33% Execution Time (edit distance) ê25% Energy ê21% -
Optimality of Two Ciphertexts Theorem (proof in ZER15 paper): Garbling
a single AND gate requires 2 ciphertexts if garbling scheme is “linear”. “linear” operations: xor, polynomial interpolation -
How to Do Better? • Non-linear operations • Gates that
are not binary – chunk-ing circuit • Boolean logic • Reusable ciphertexts • Different security assumptions • … -
Garble Encode Evaluate Decode f garbled circuit F e X
Y f(x) d x Security properties Privacy: F, X, and d leak reveals nothing beyond f(x) Obliviousness: F, X reveals nothing (new) Authenticity: given F, X, hard to find Y’ such that: Decode(Y’, d) ∉ { f(x), error }